See the whole incident
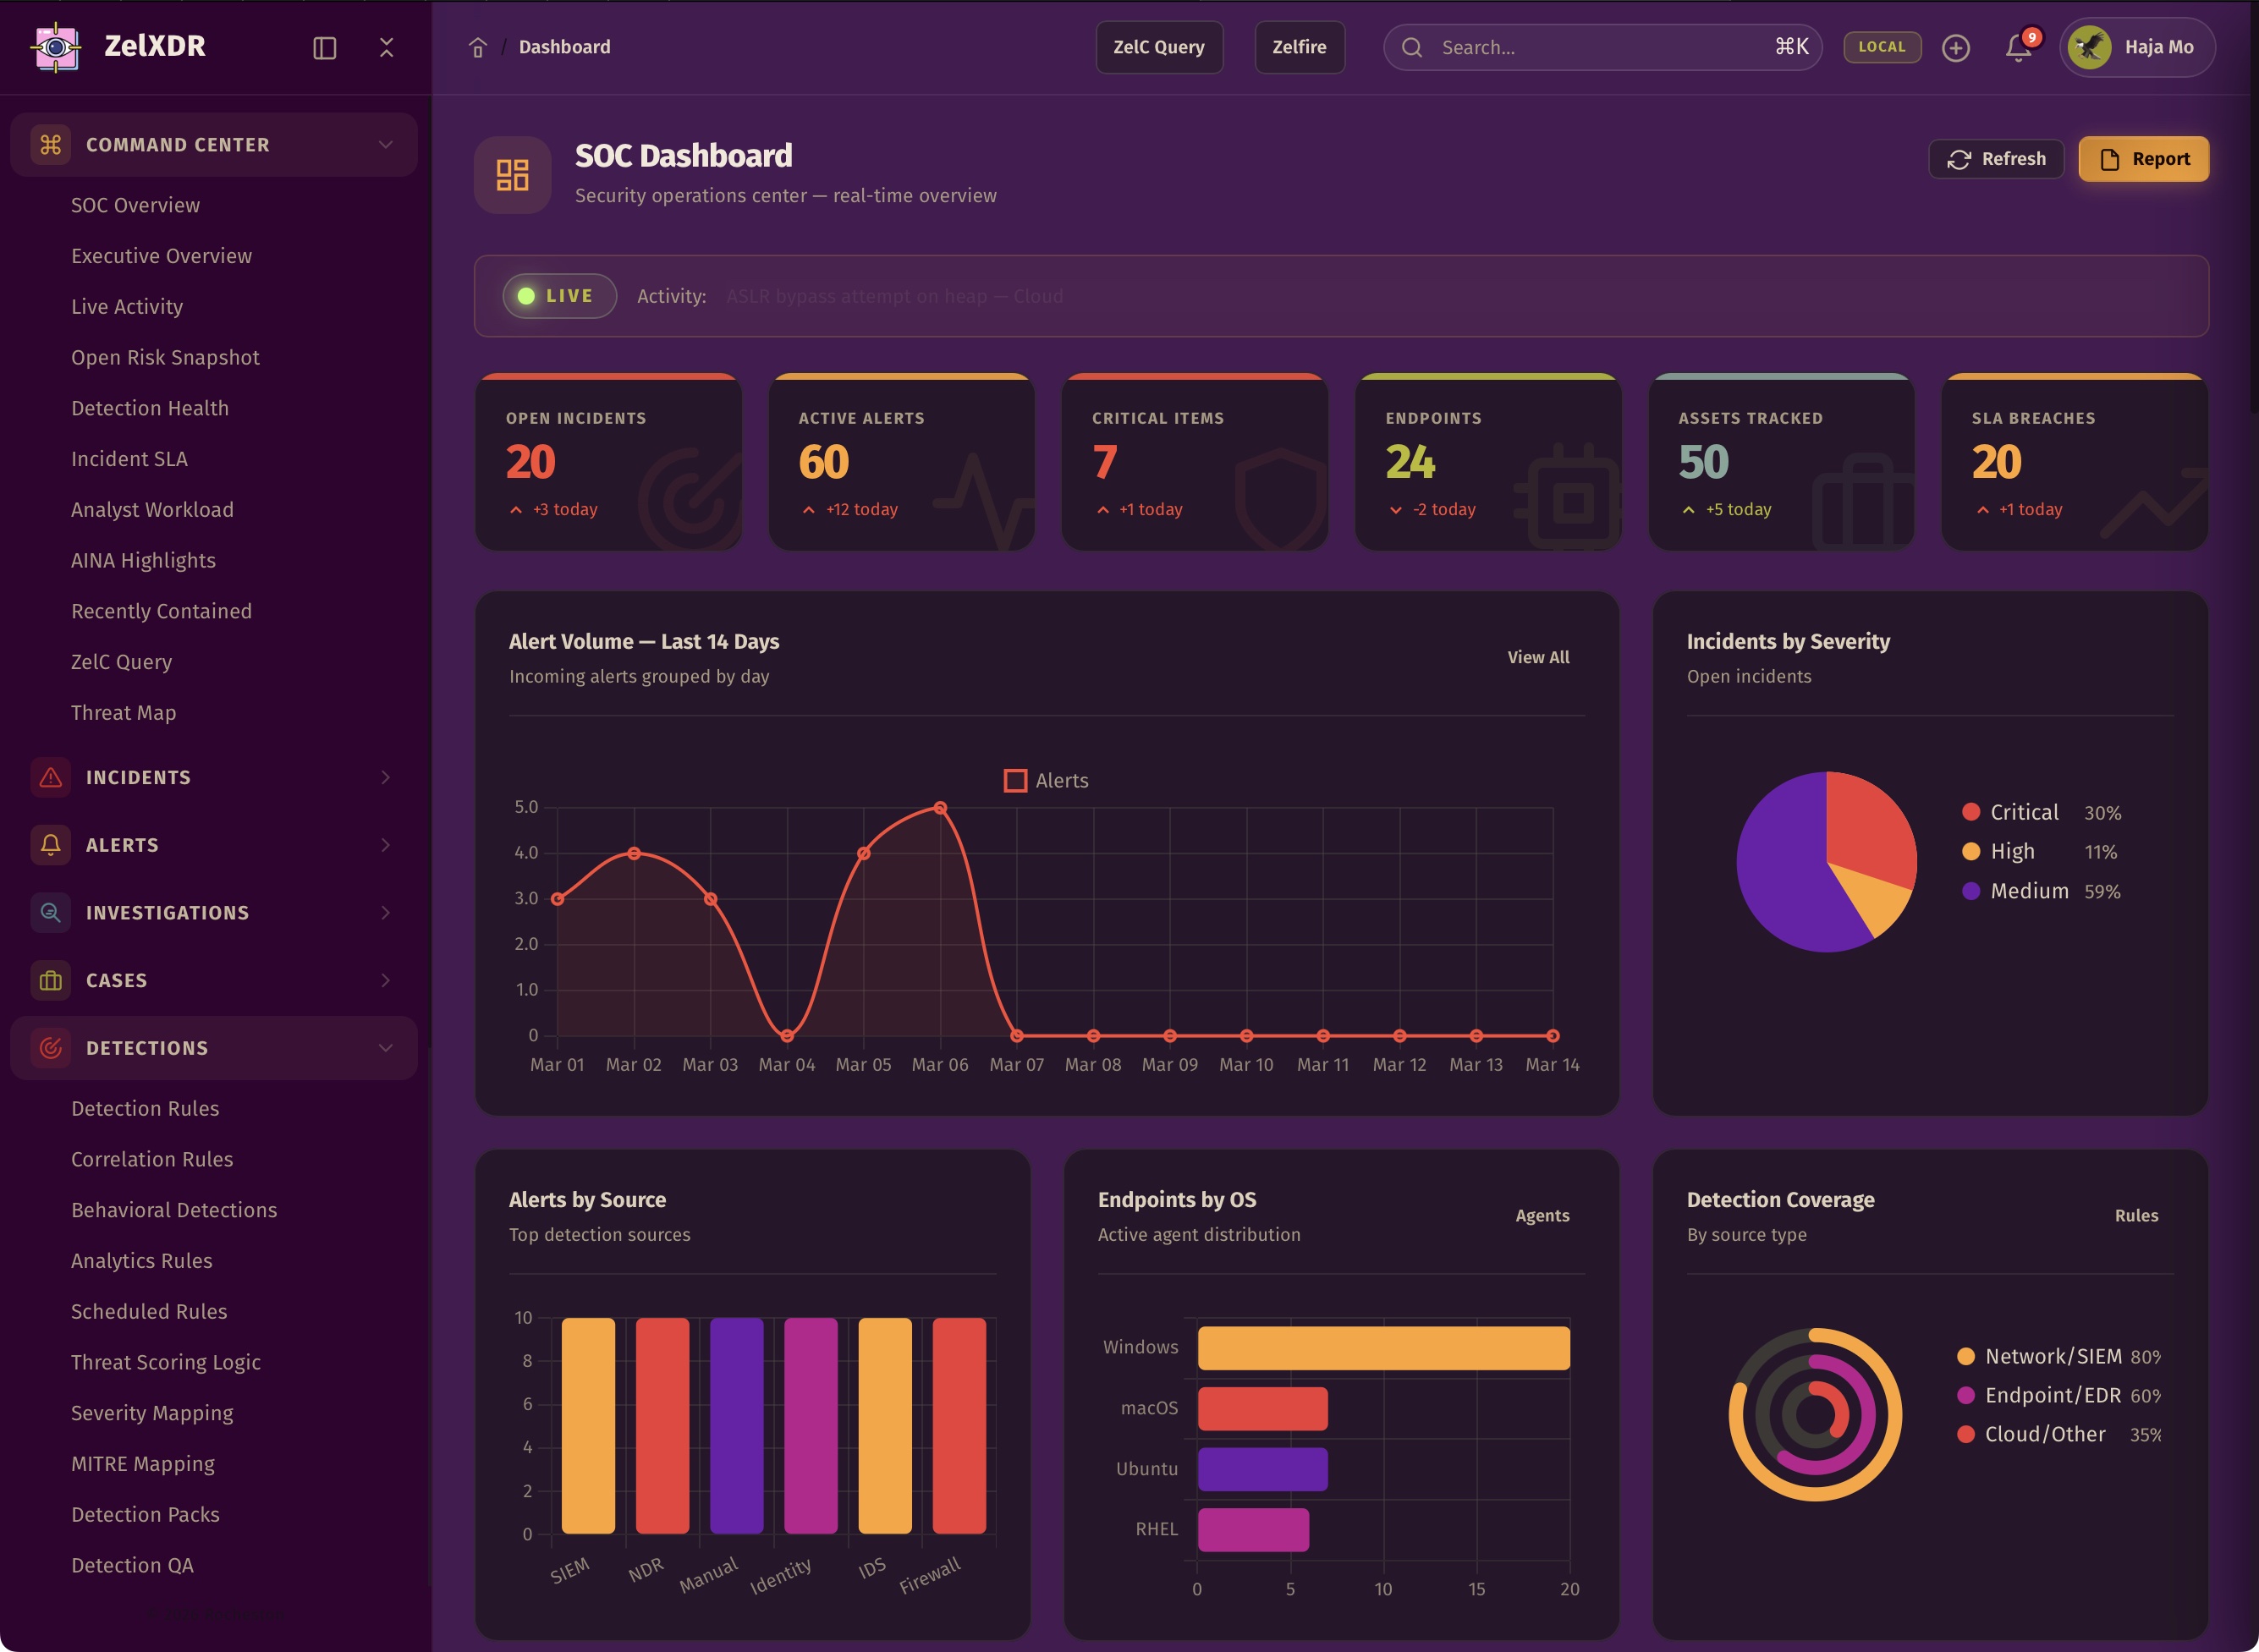
Connect alerts, endpoints, and telemetry into a unified operational view.
DETECTION & RESPONSE
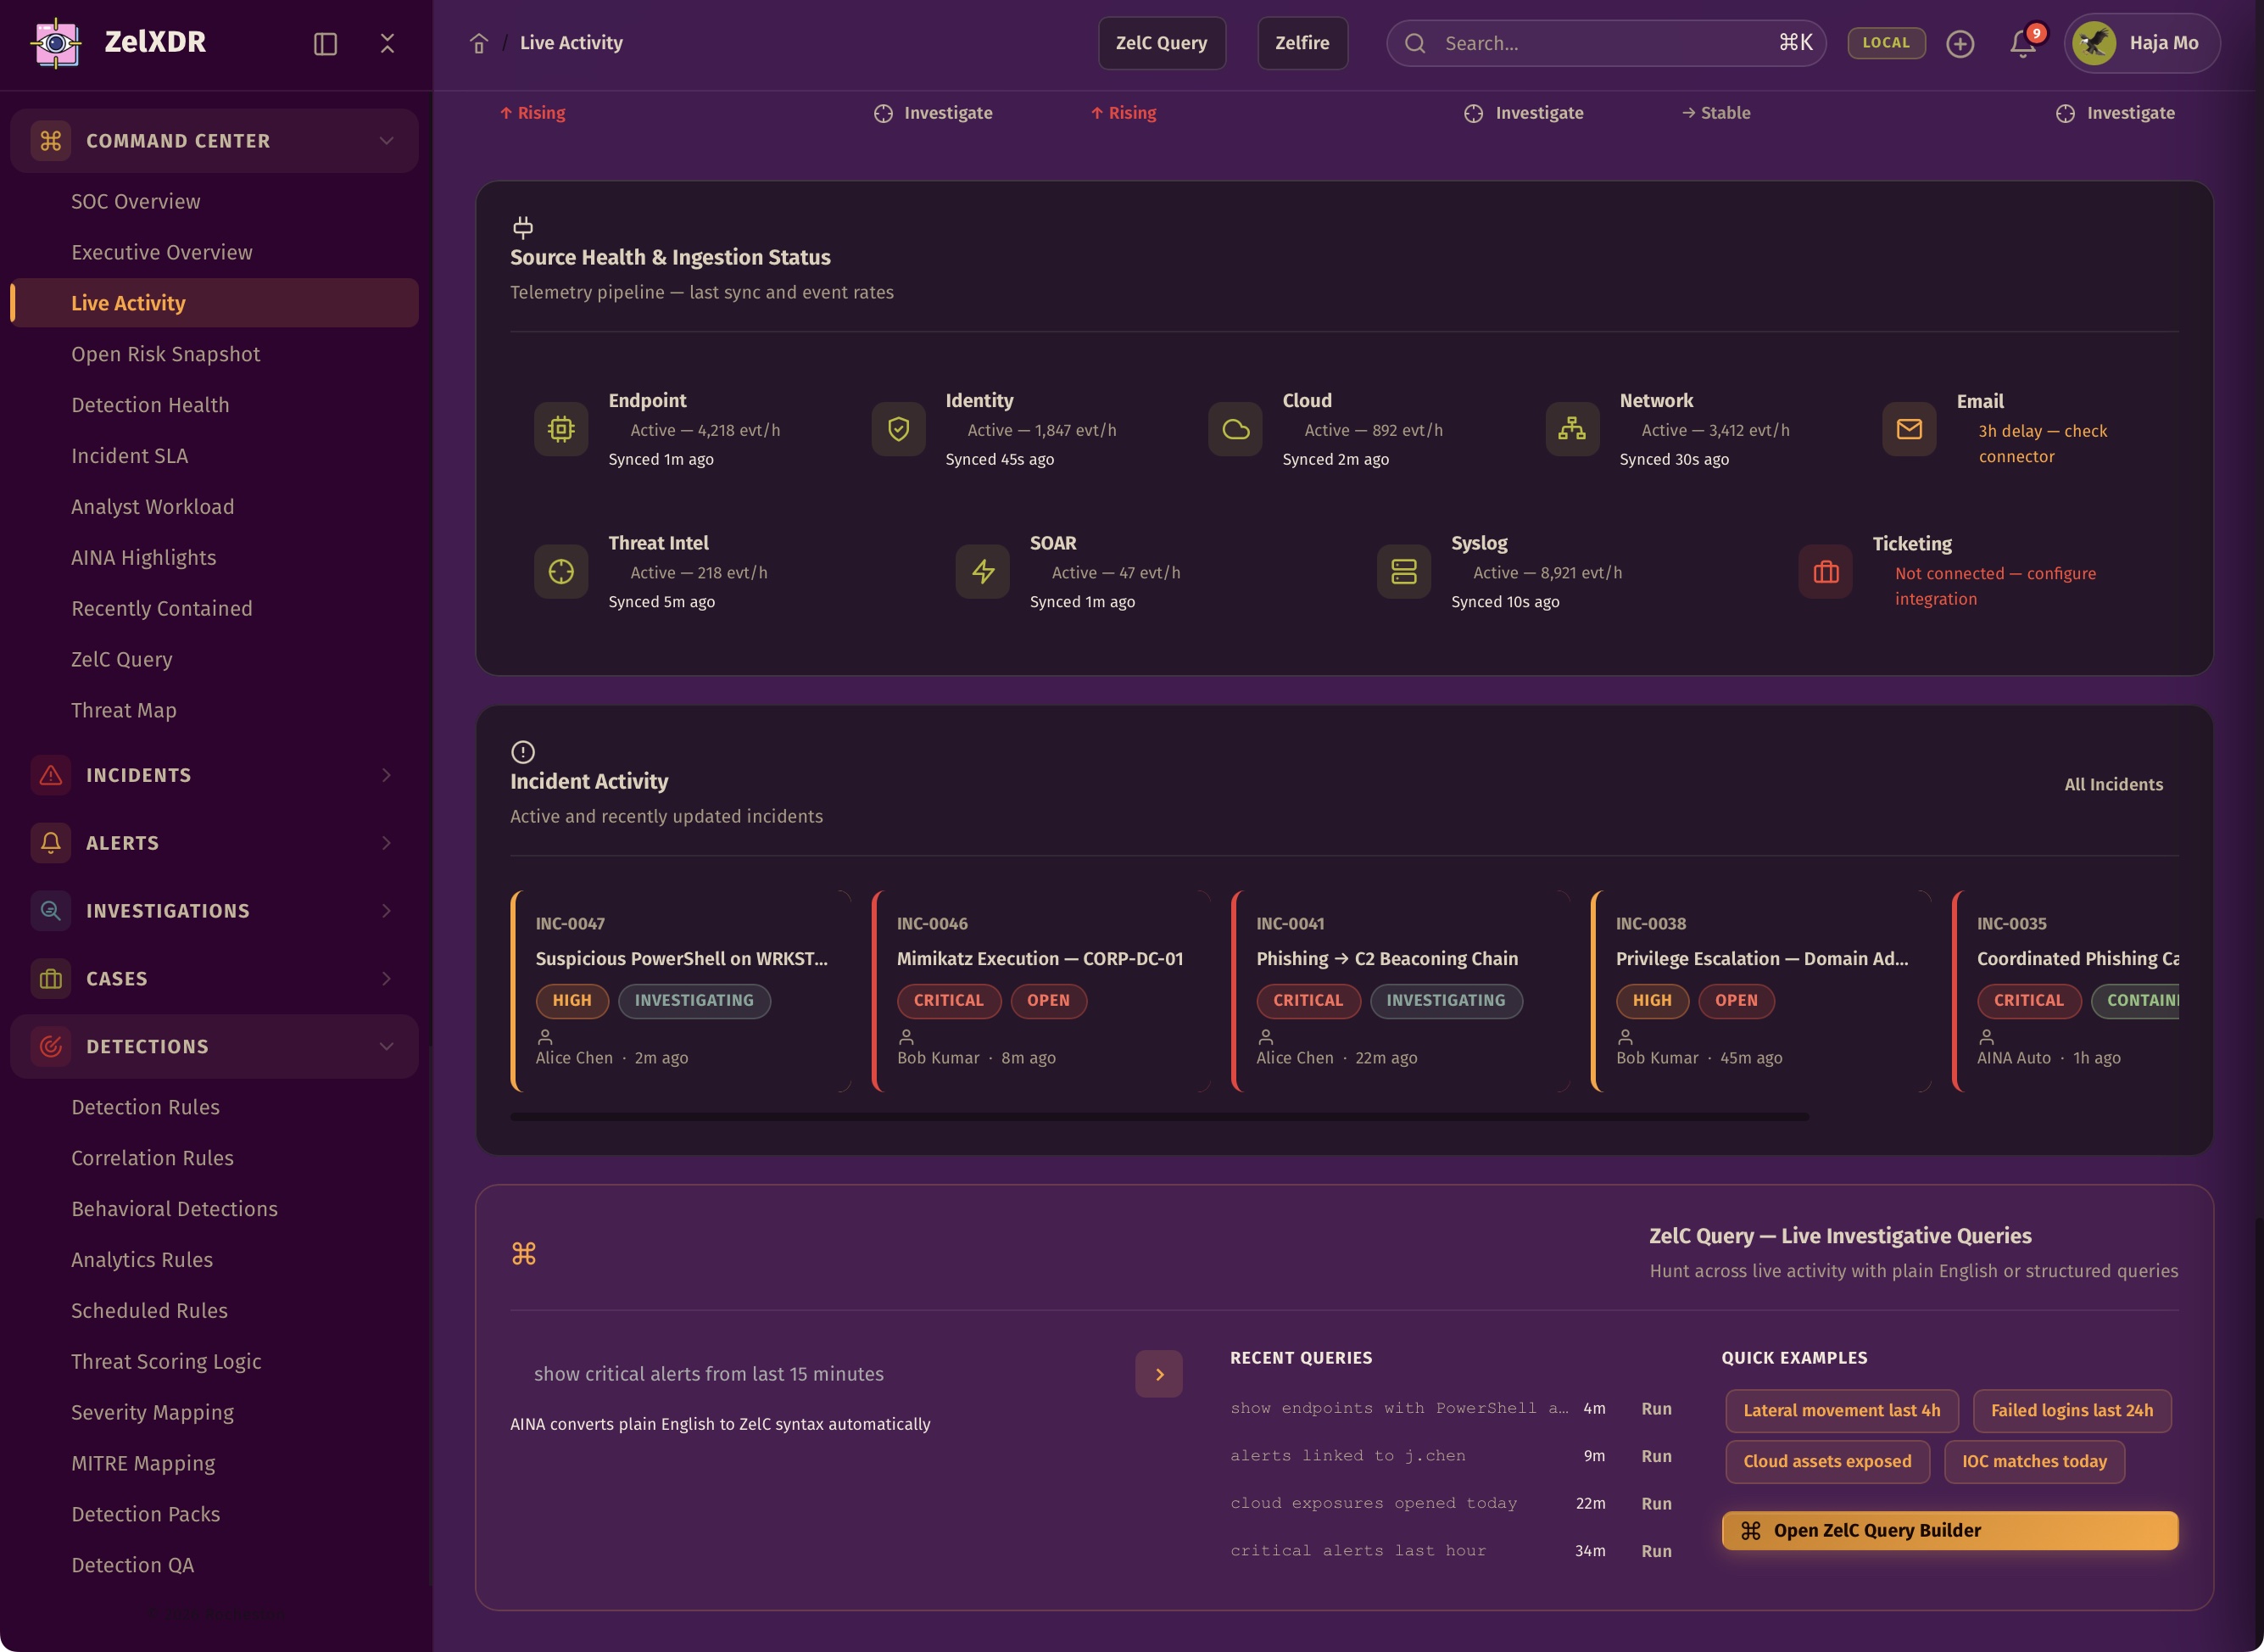
Bring alerts, incidents, endpoints, telemetry, investigations, and threat hunting into one security workspace. AINA helps your team triage the noise, understand the evidence, and coordinate response.
One command surface, from detection to response.
BUILT FOR YOUR WORKFLOW
Connect alerts, endpoints, and telemetry into a unified operational view.
Summarize alerts, cluster related signals, and get guidance for the next step.
Move from investigation to threat hunting and response with the evidence in context.
THE COMPLETE PRODUCT GUIDE
Get to know the capabilities, workflows, and intelligence behind the product.
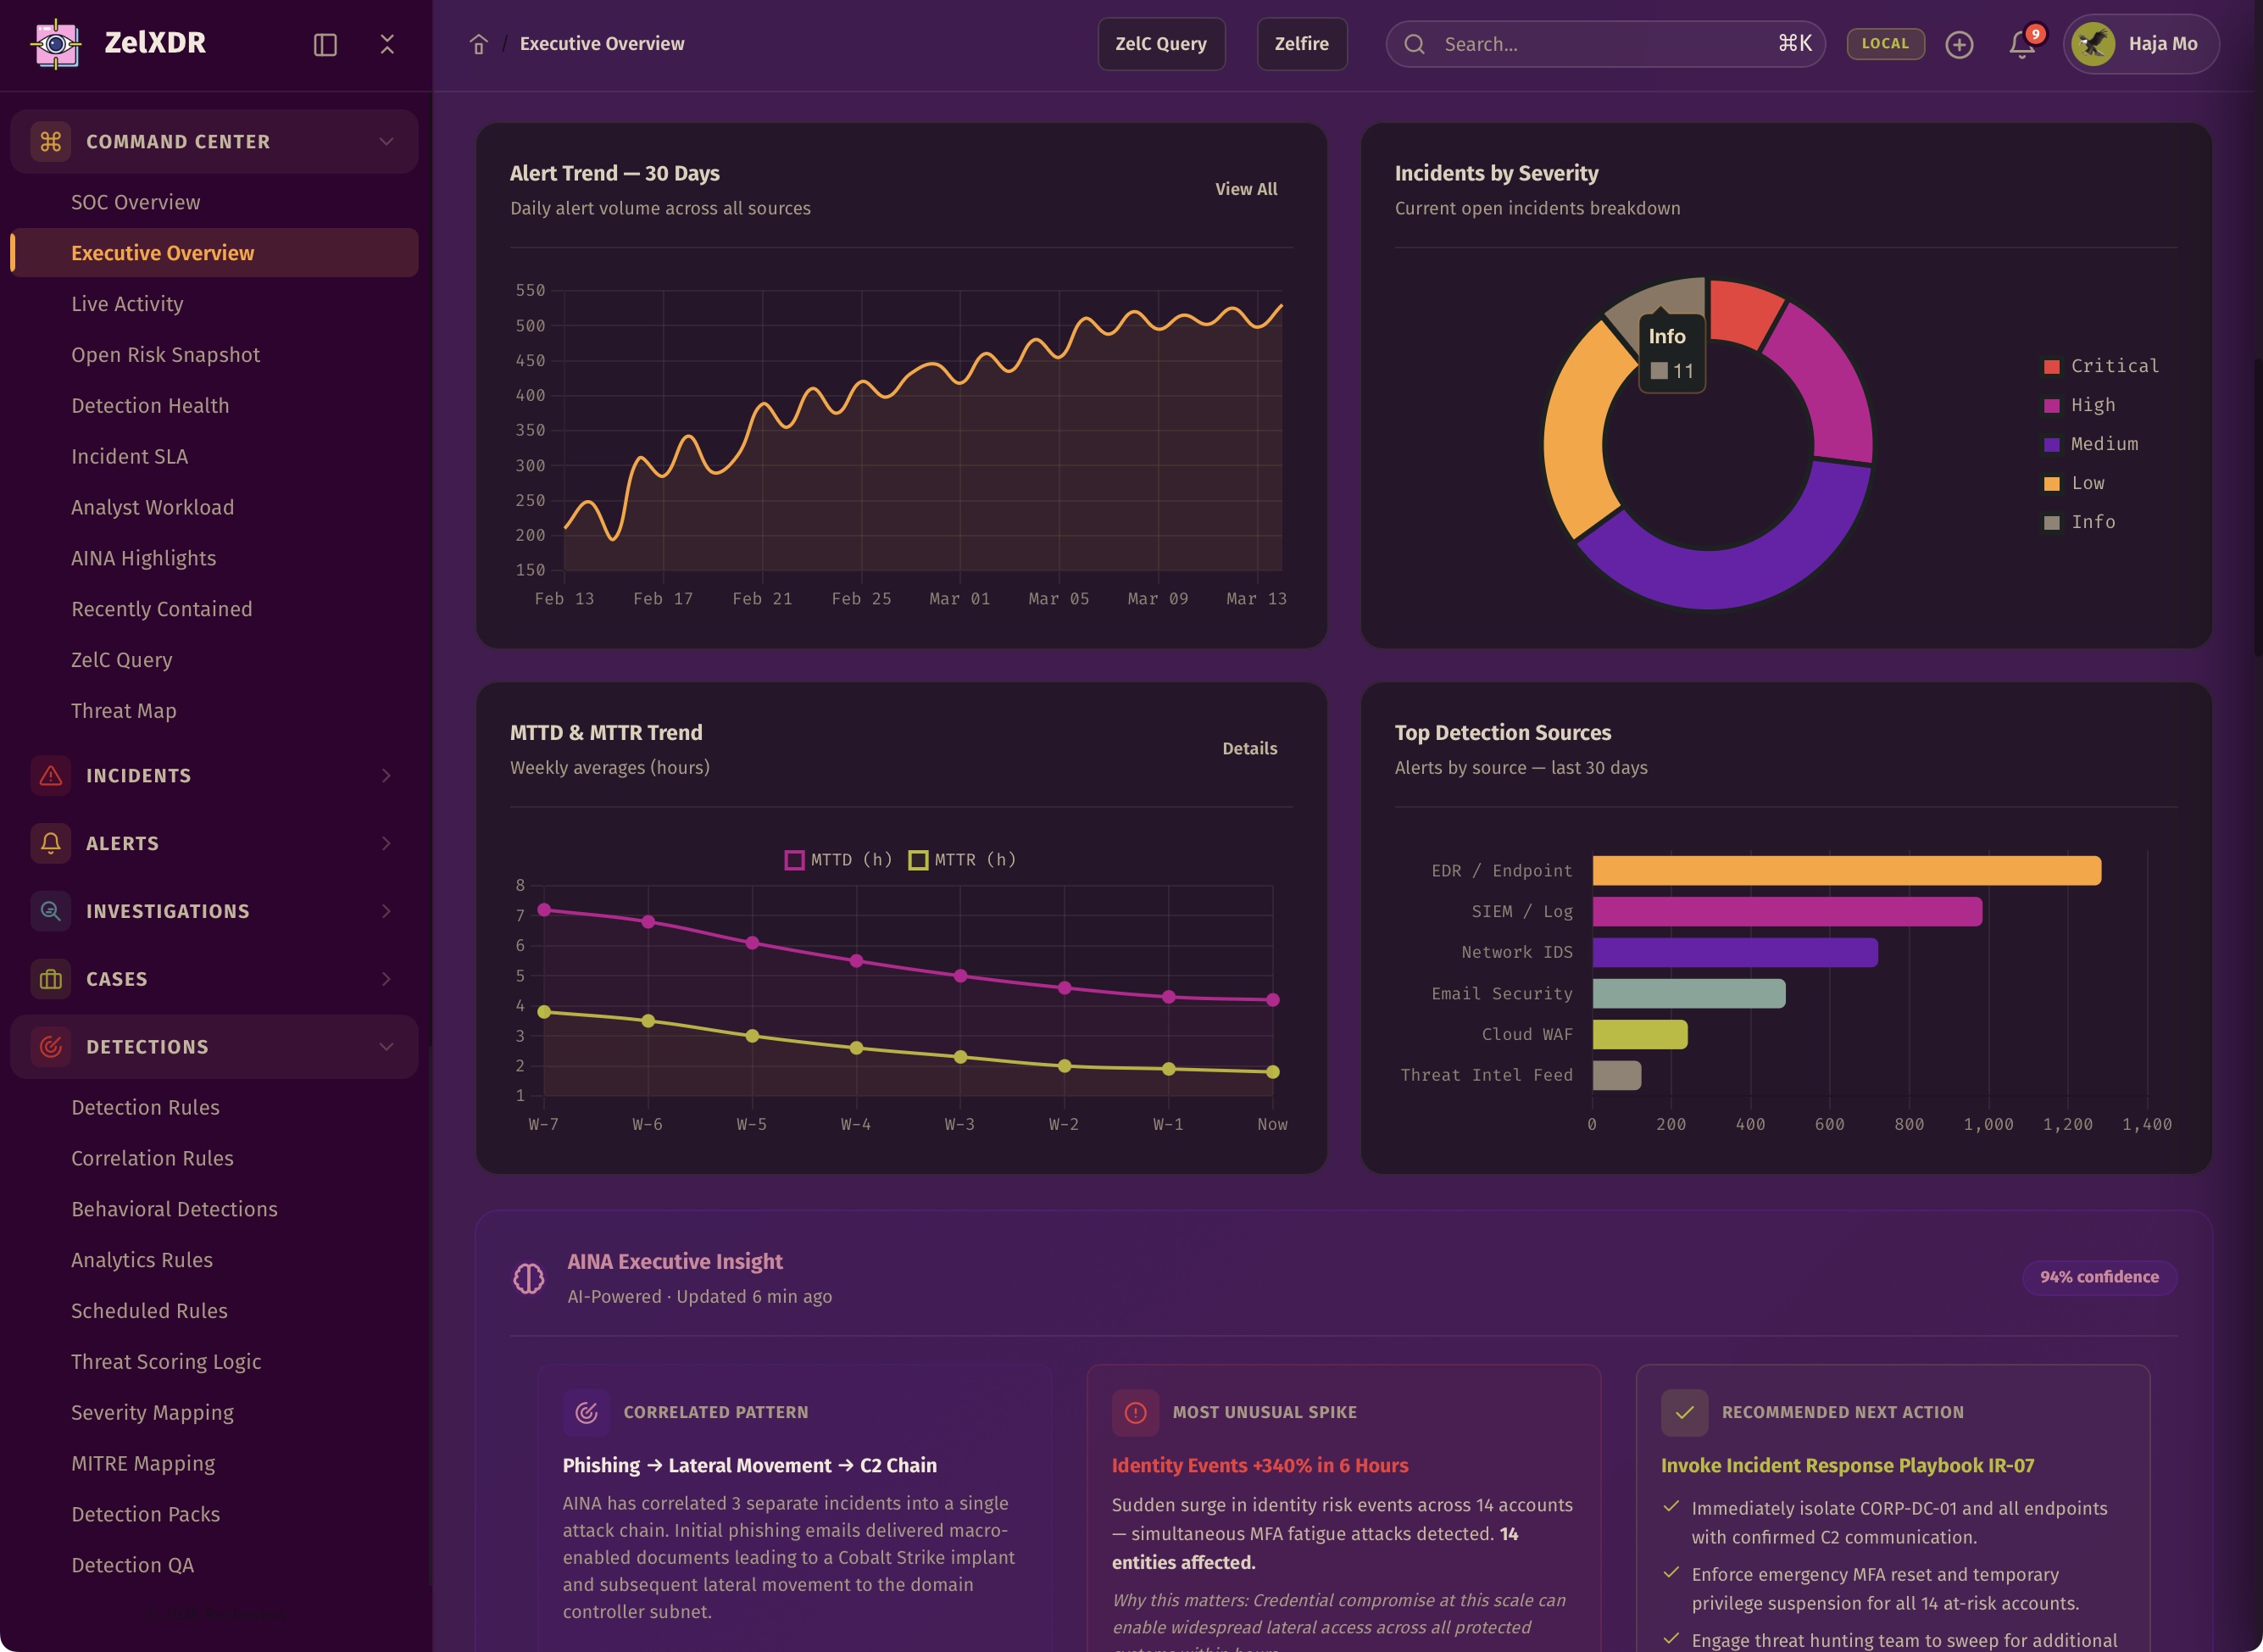
ZelXDR is the intelligent command layer for modern security operations. It brings alerts, incidents, telemetry, endpoints, investigations, threat hunting, and AI-driven analysis into one unified platform, helping teams move from noise to clarity and from detection to decisive action.
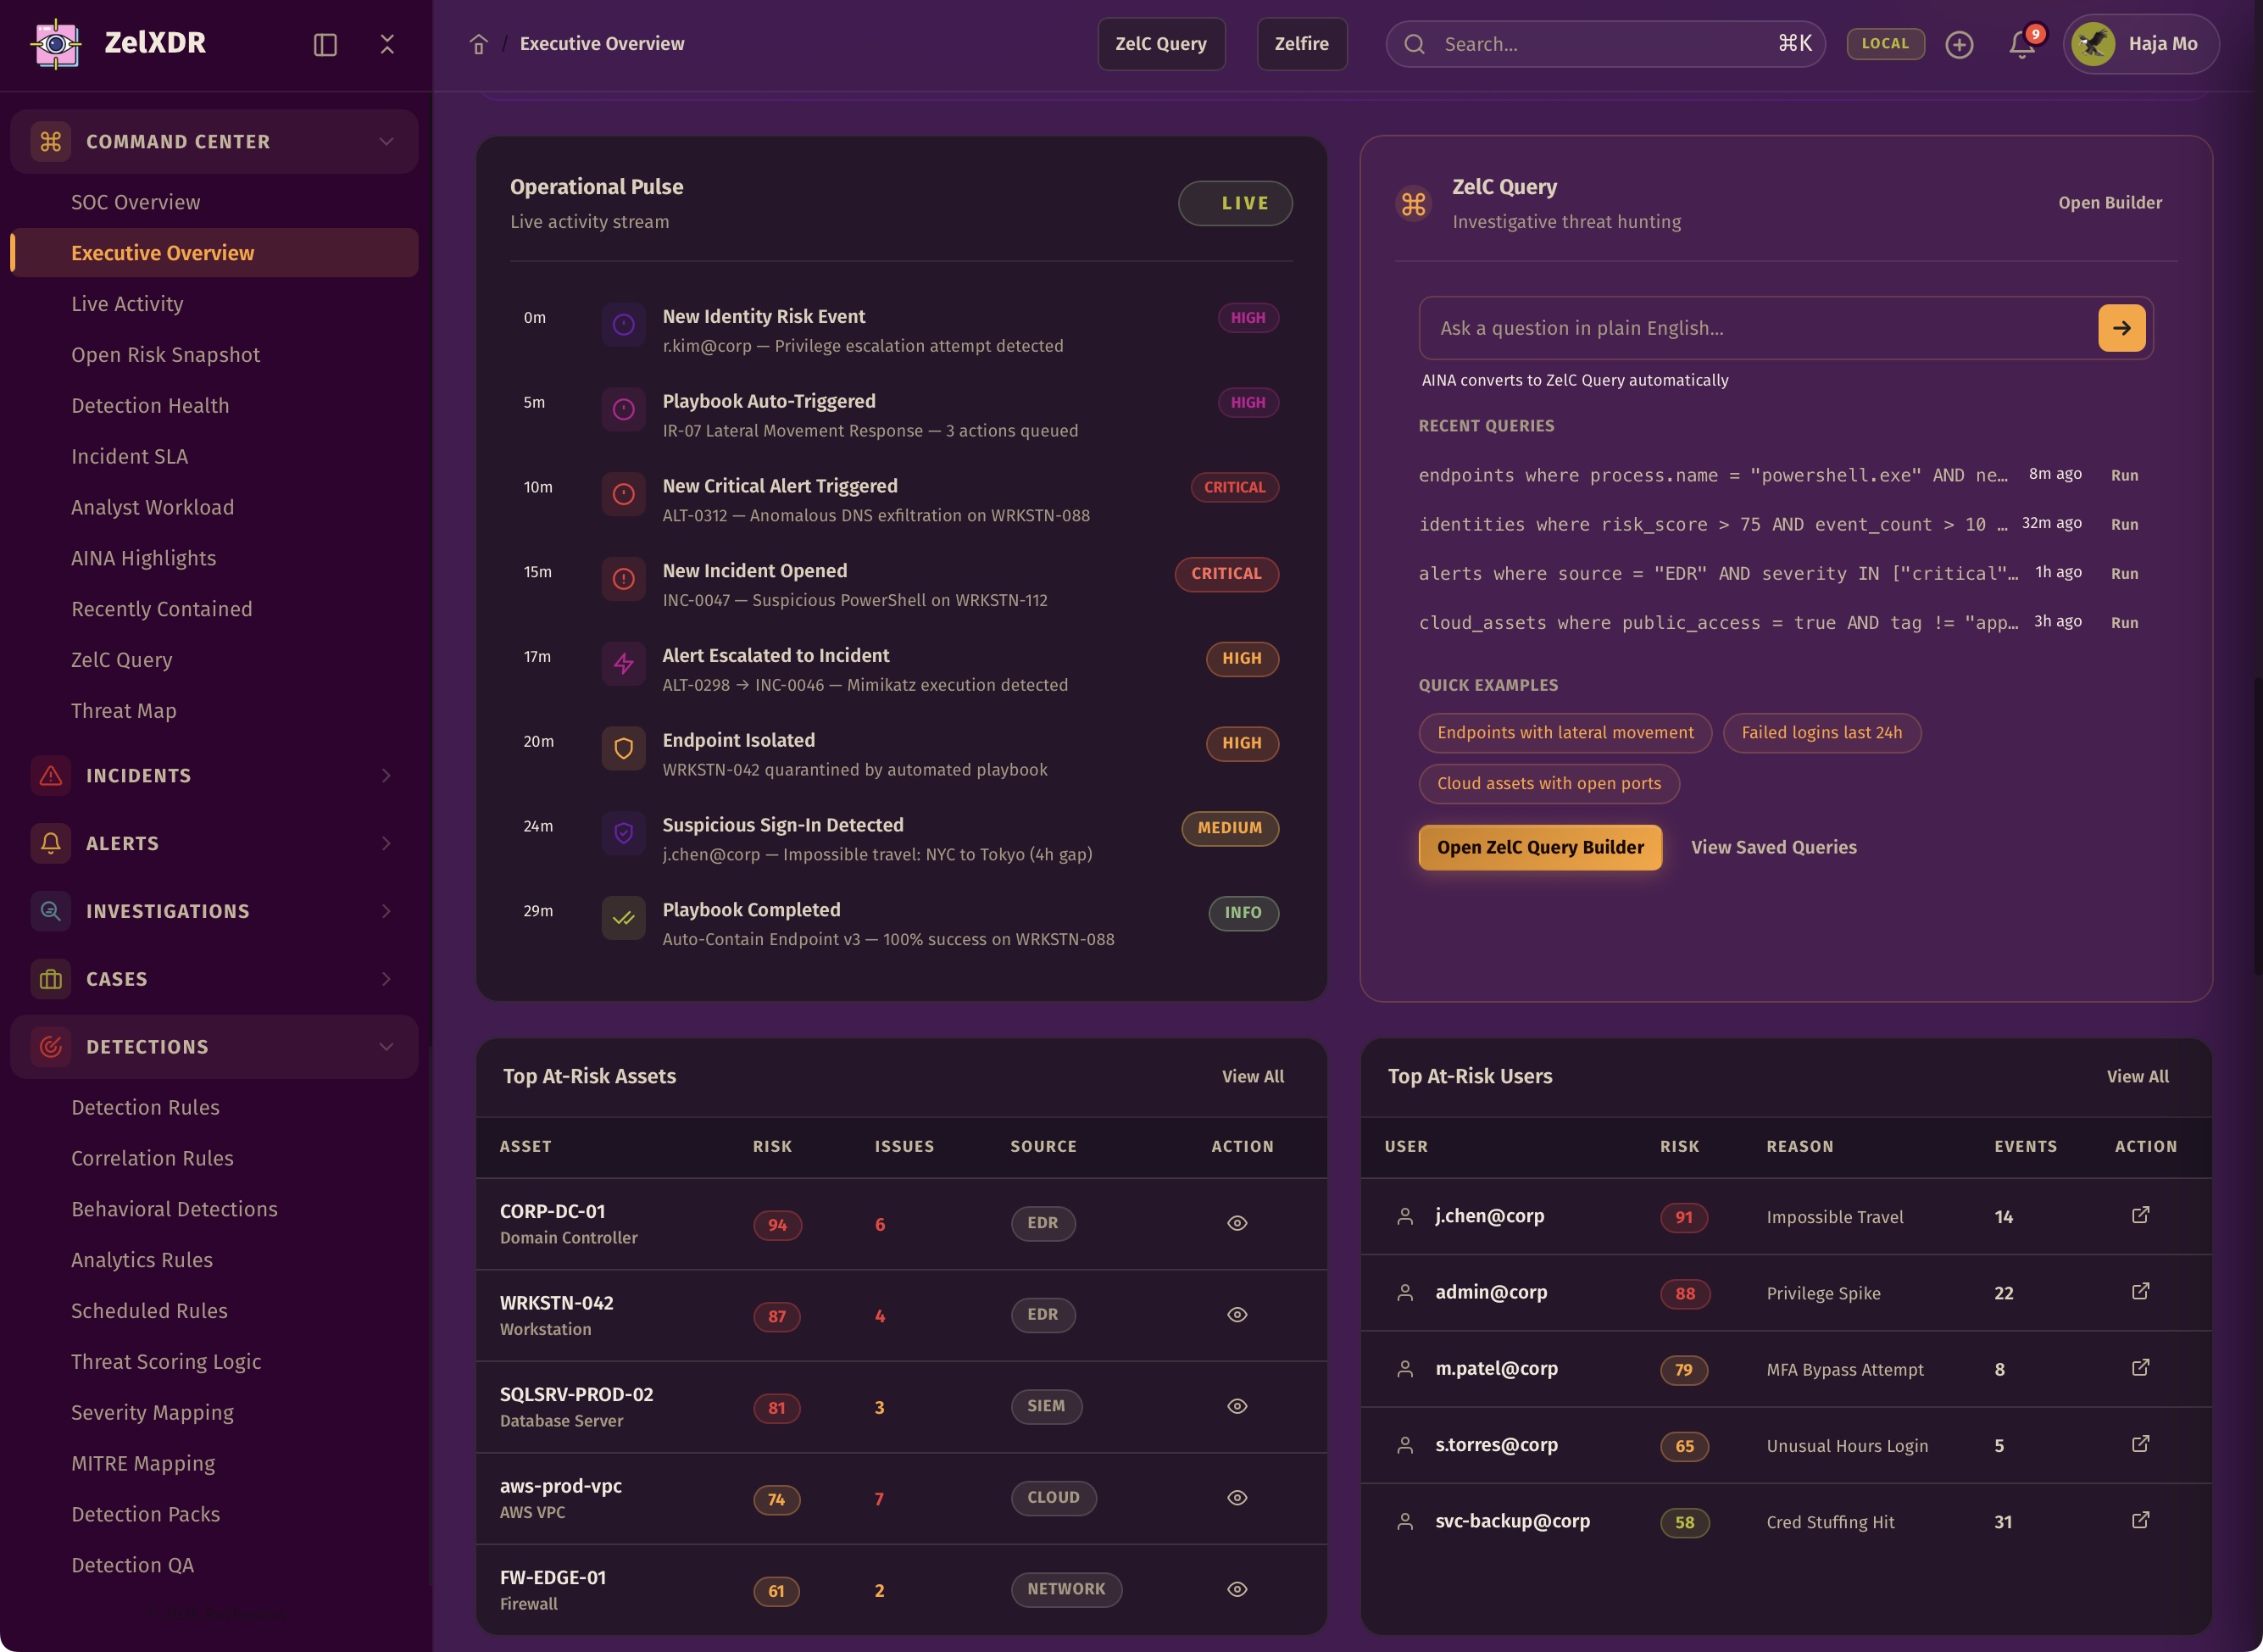
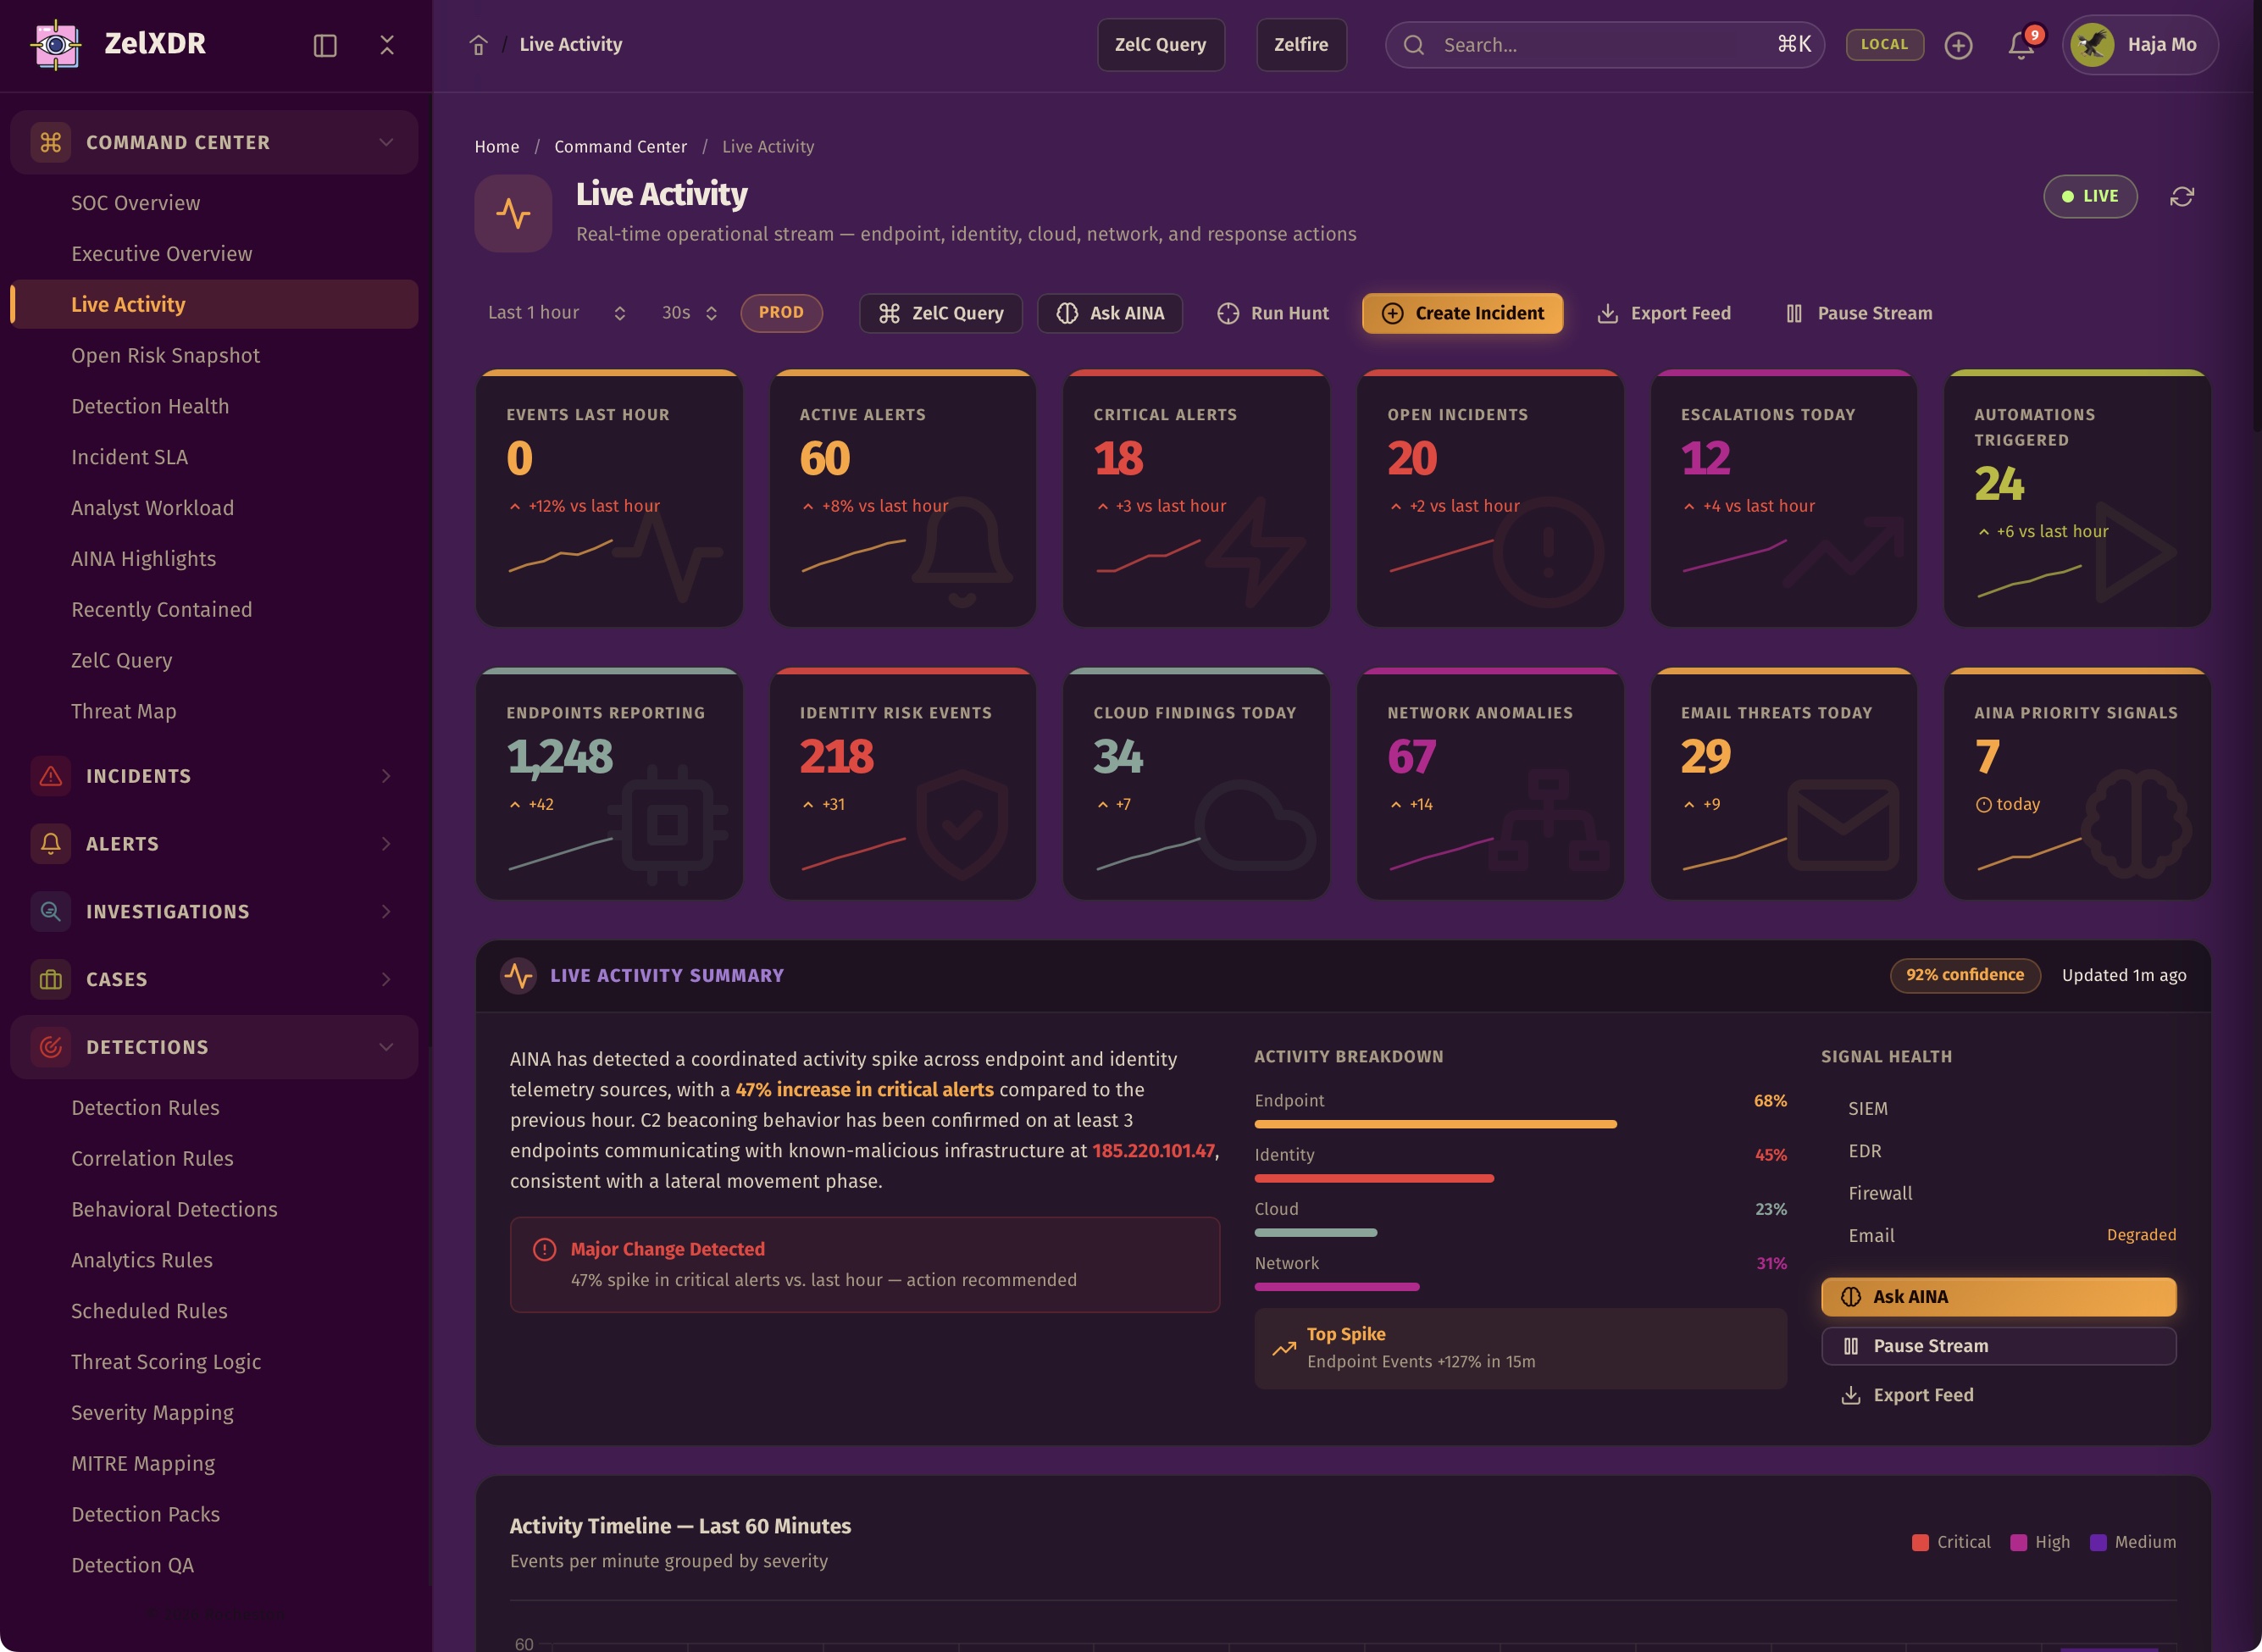
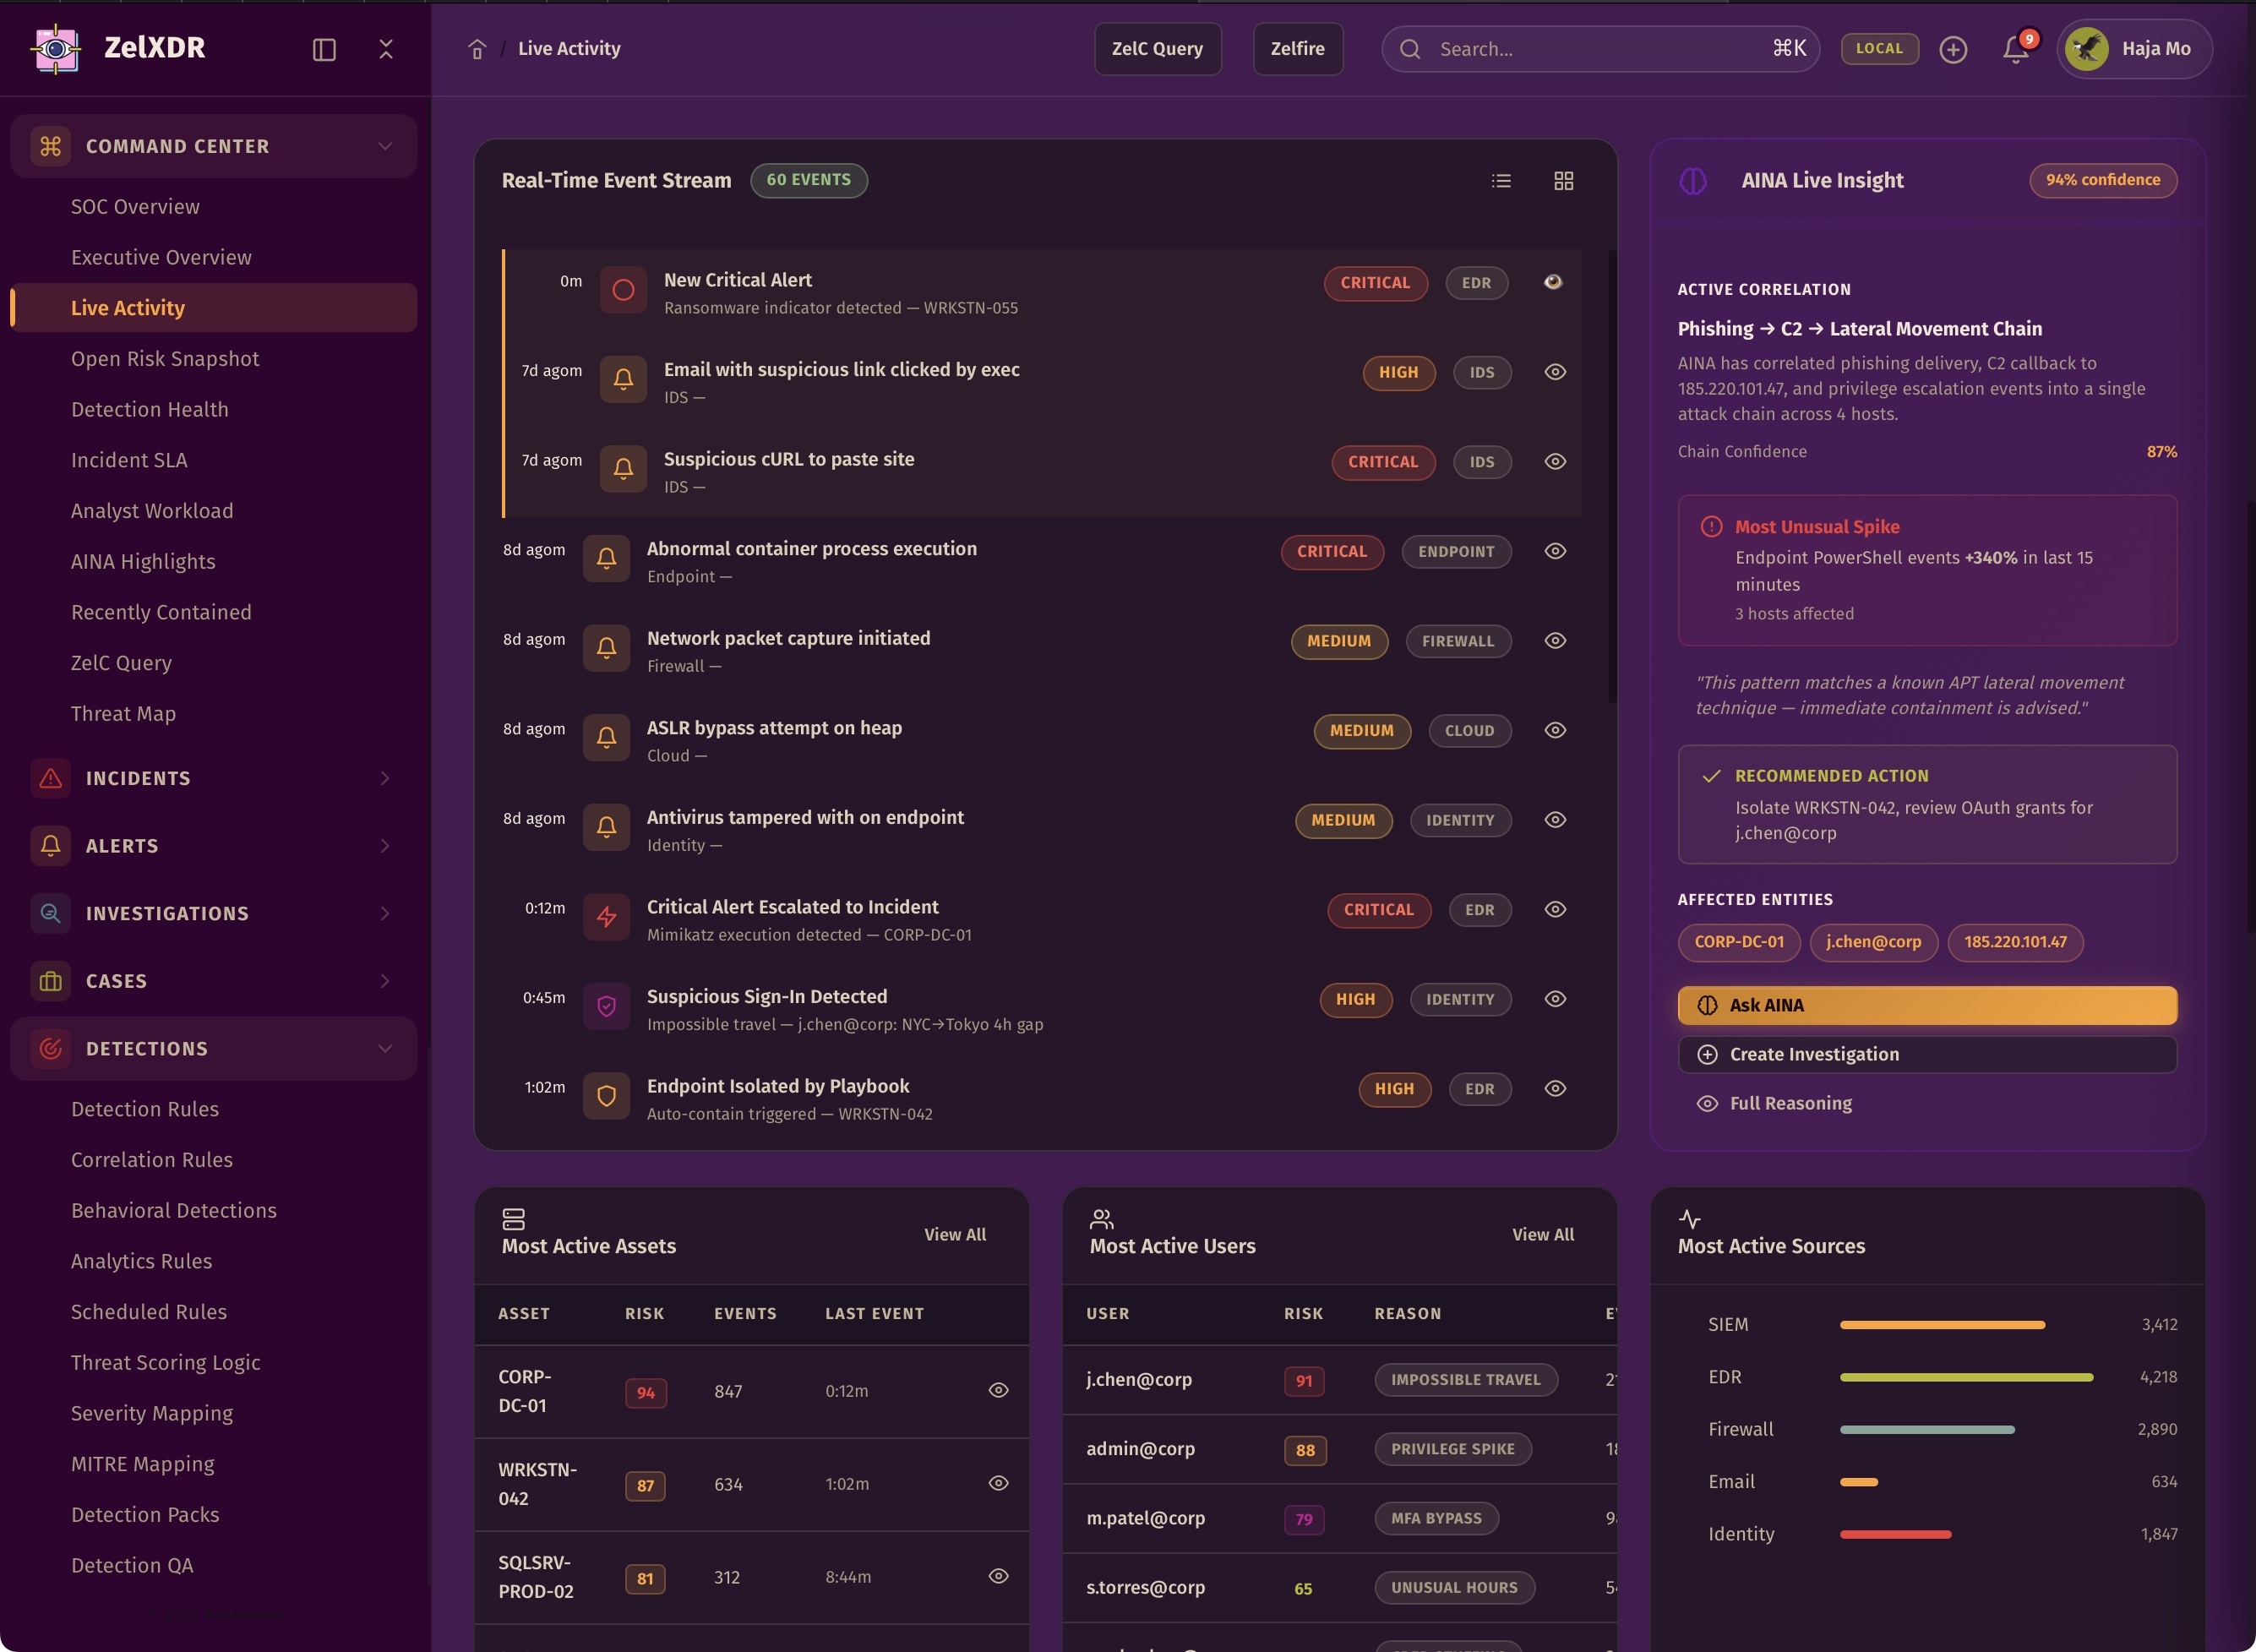
ZelXDR brings alerts, incidents, endpoints, hunts, telemetry, AI reasoning, and reporting into one operational experience. It gives defenders a single place to see what matters, understand what is happening, and act with confidence.
One command surface. One security story. One place to act.
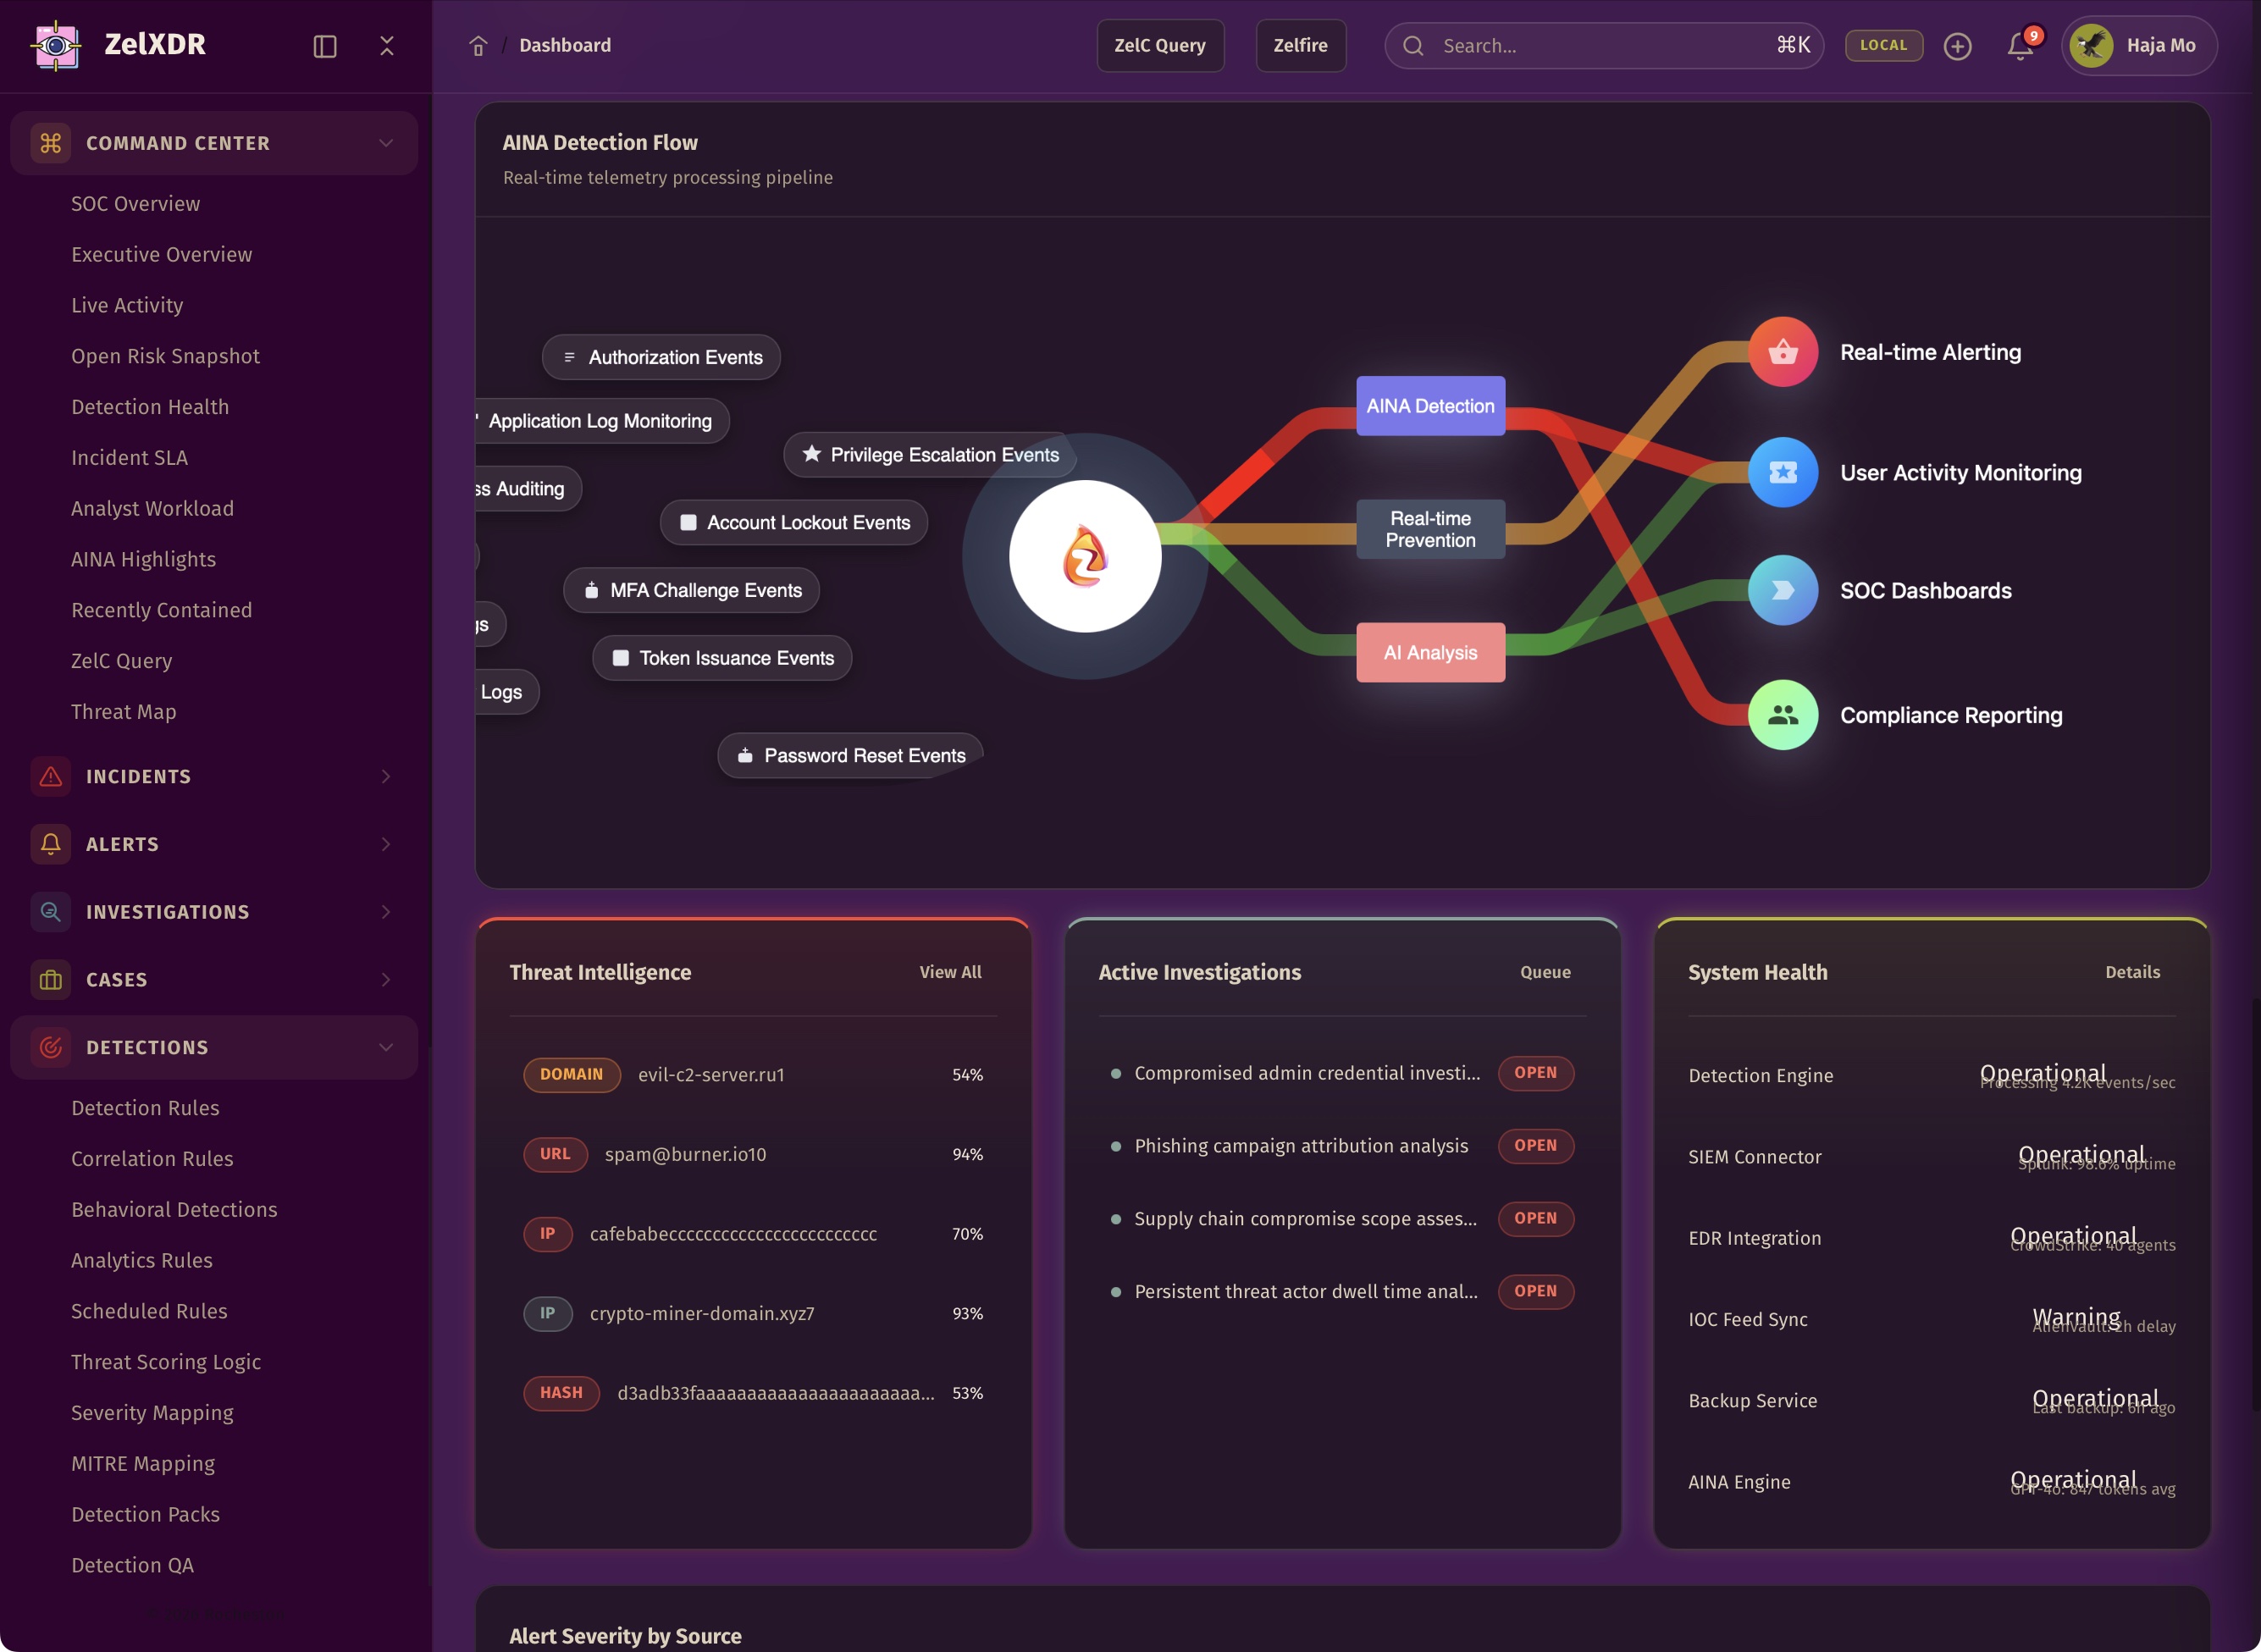
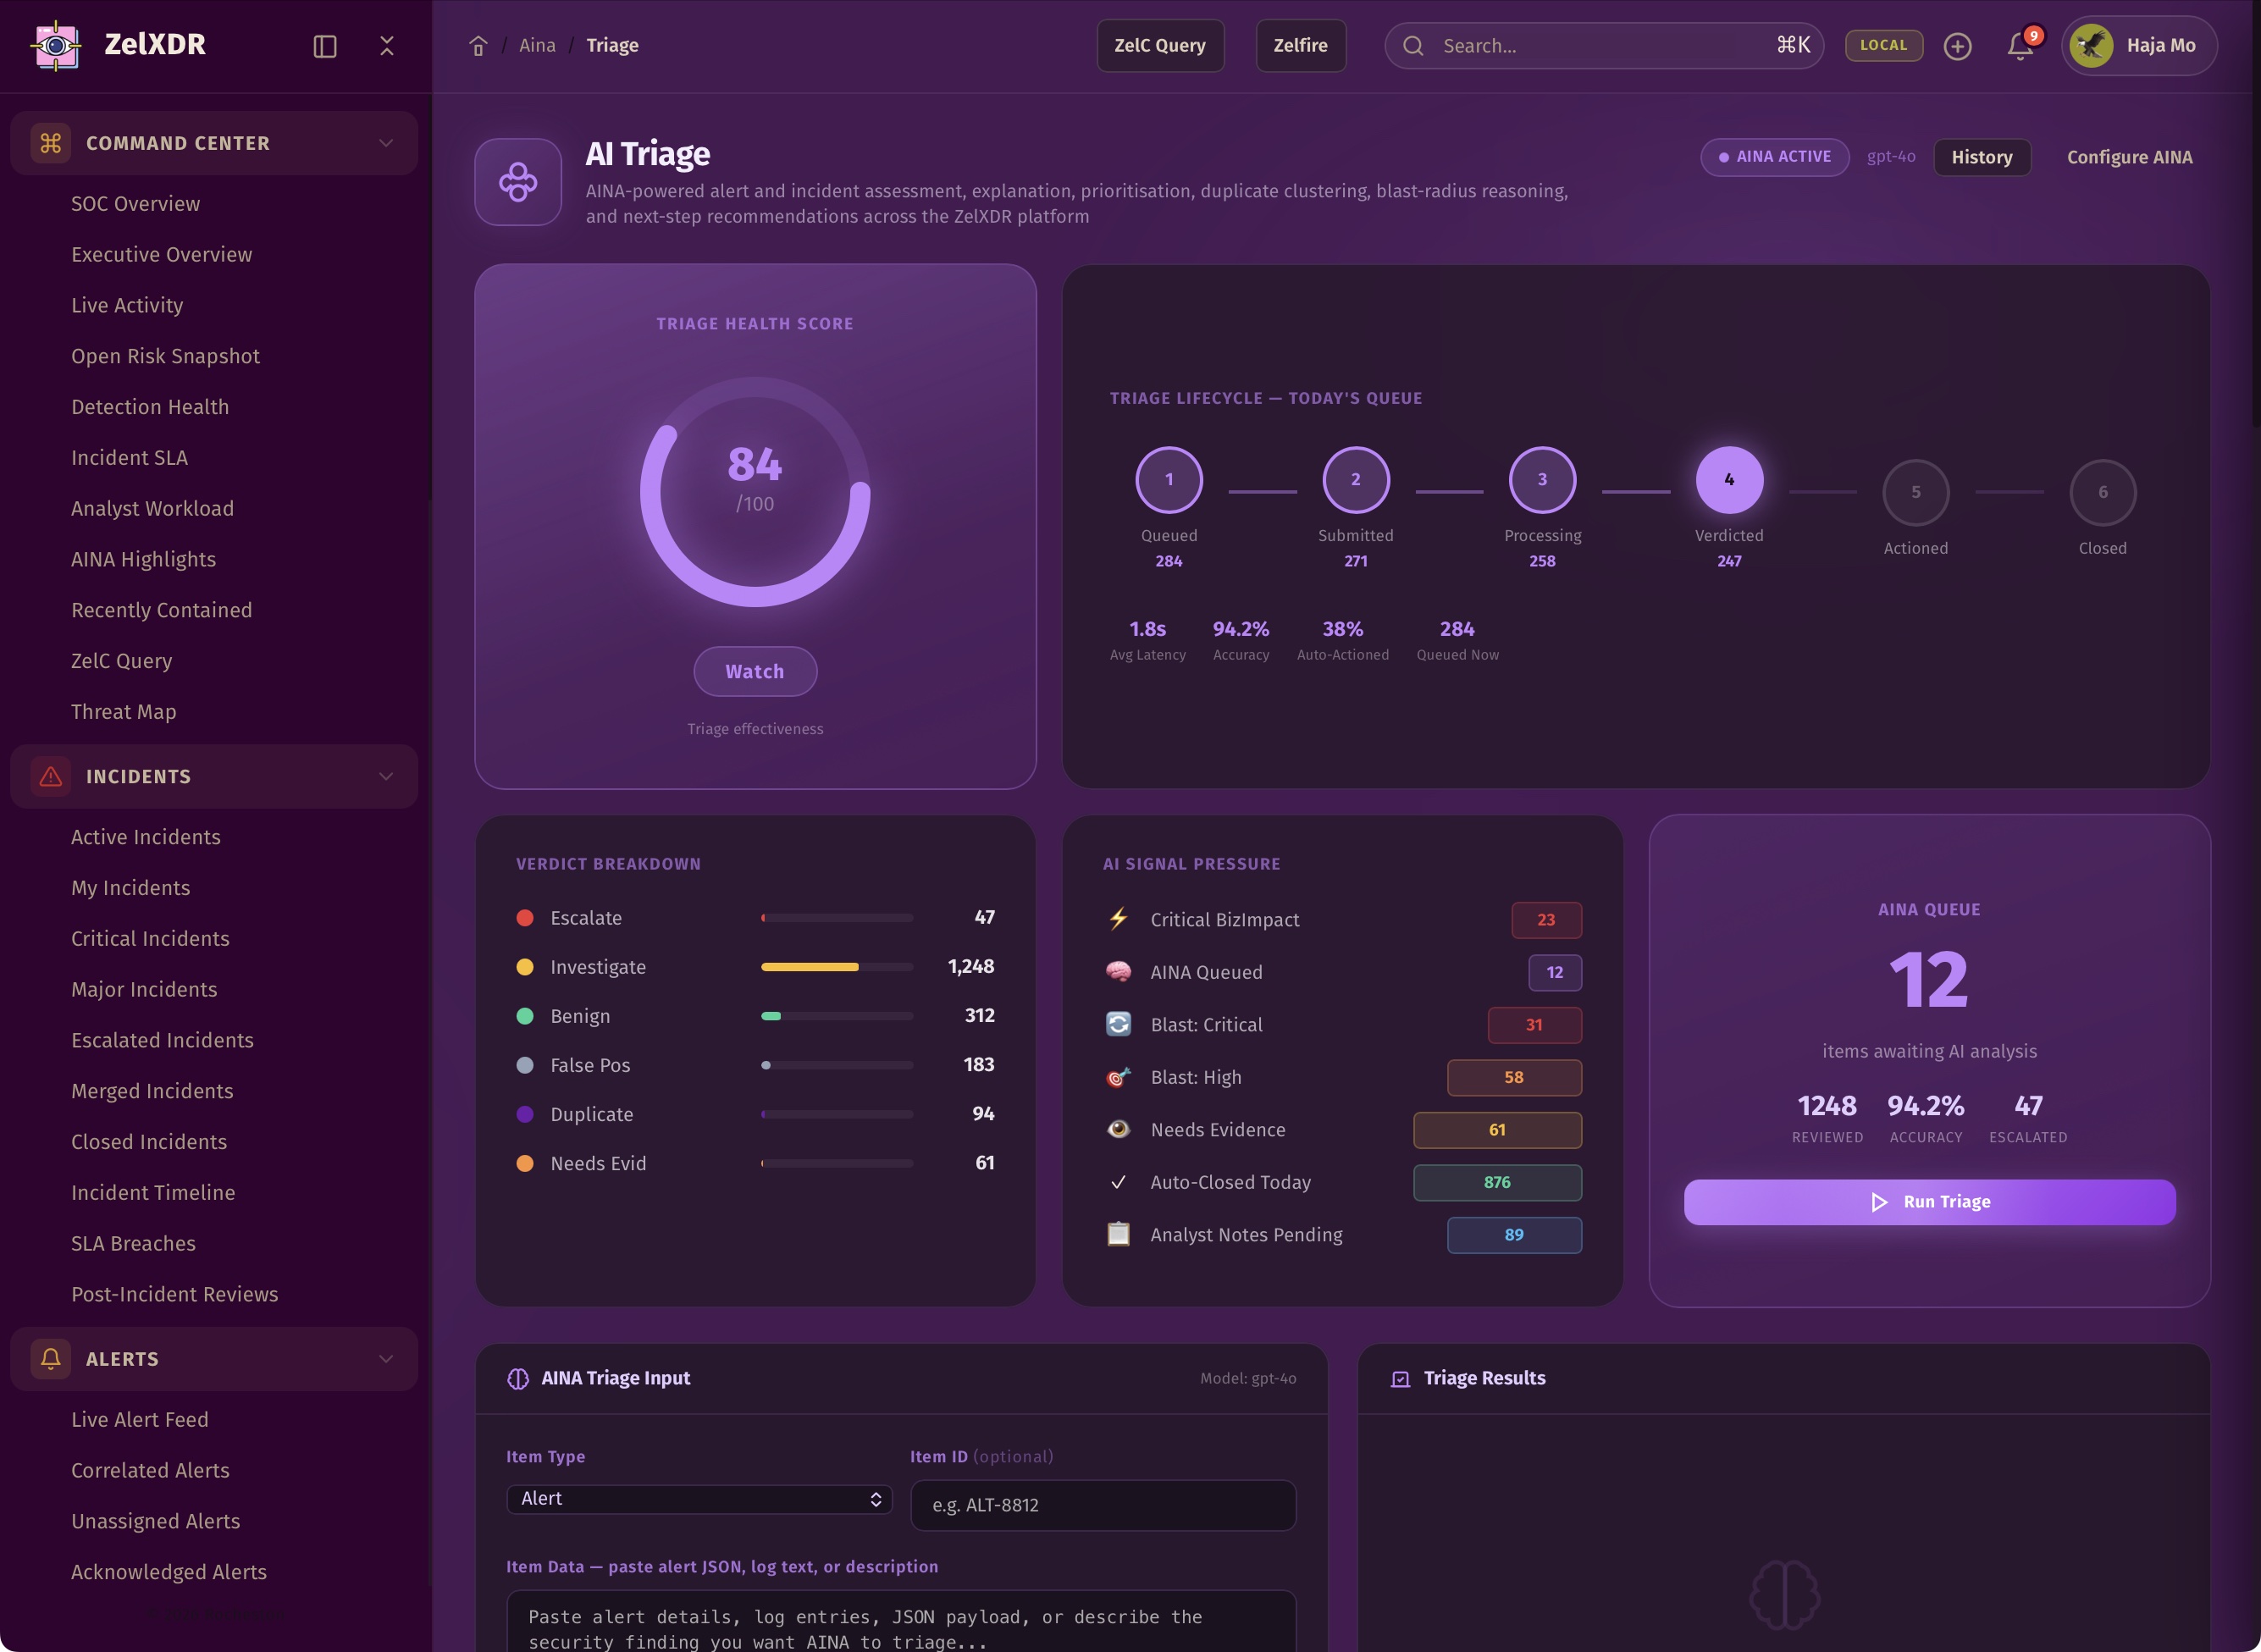
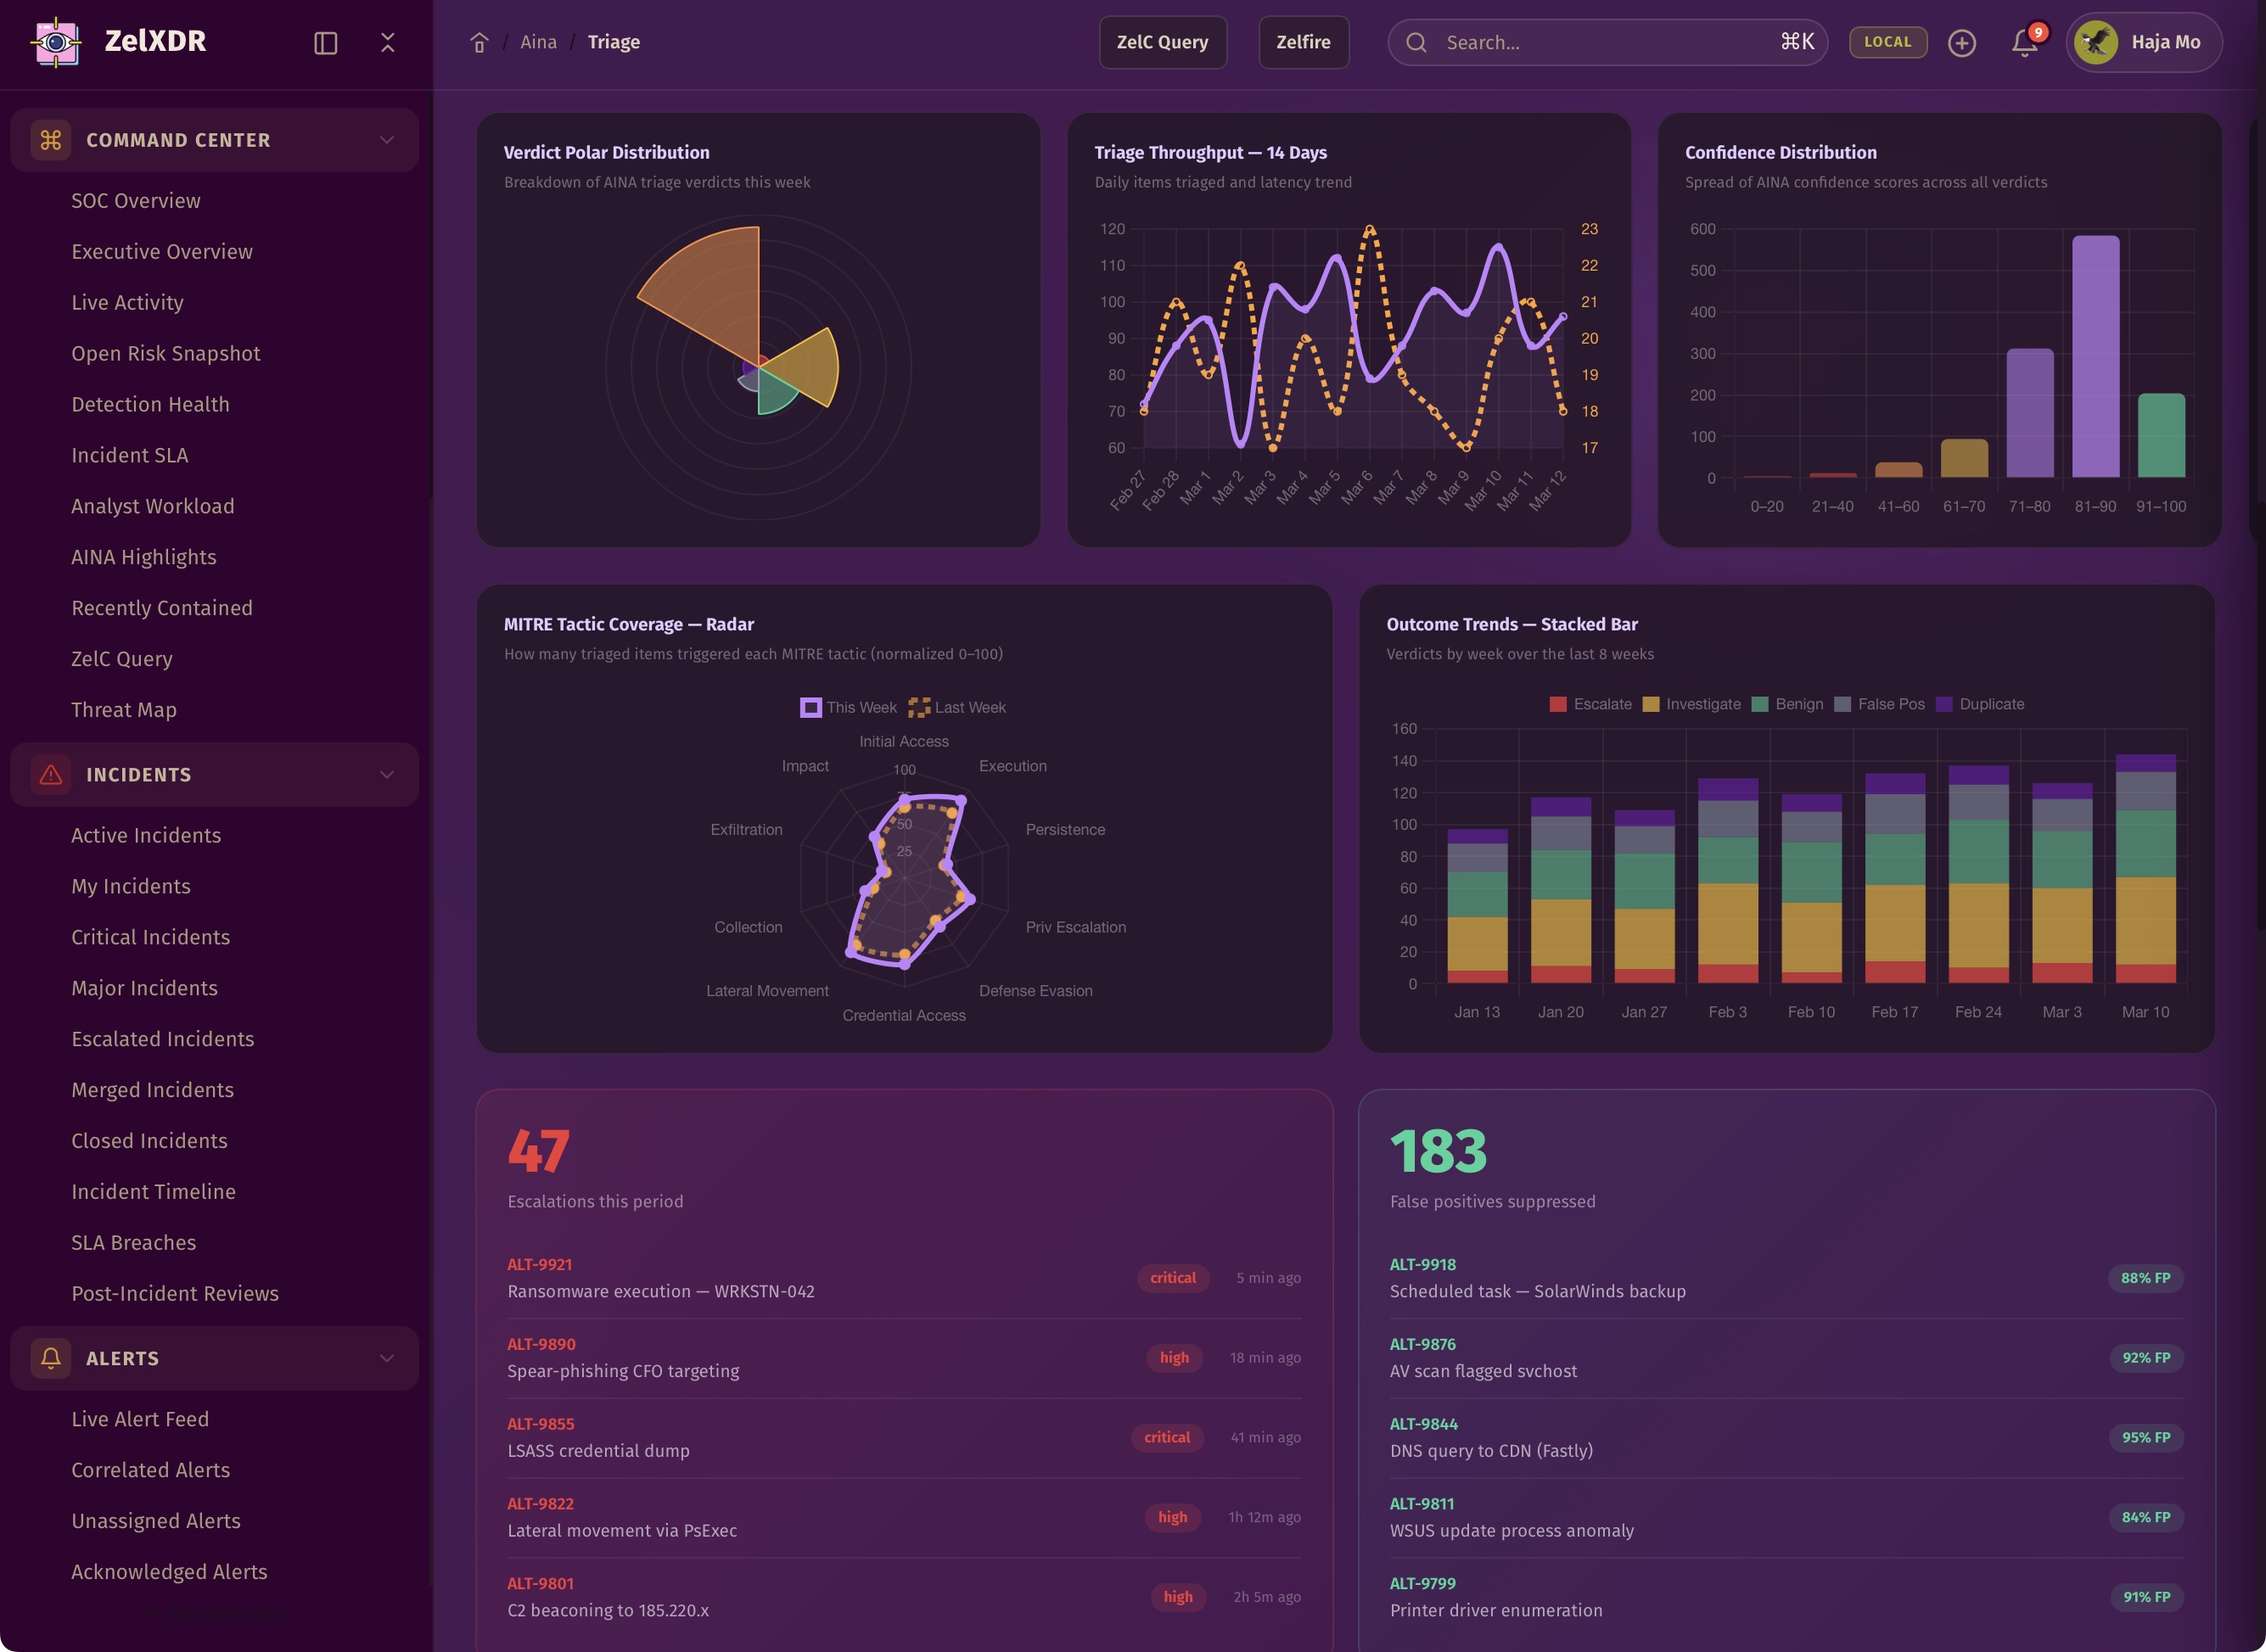
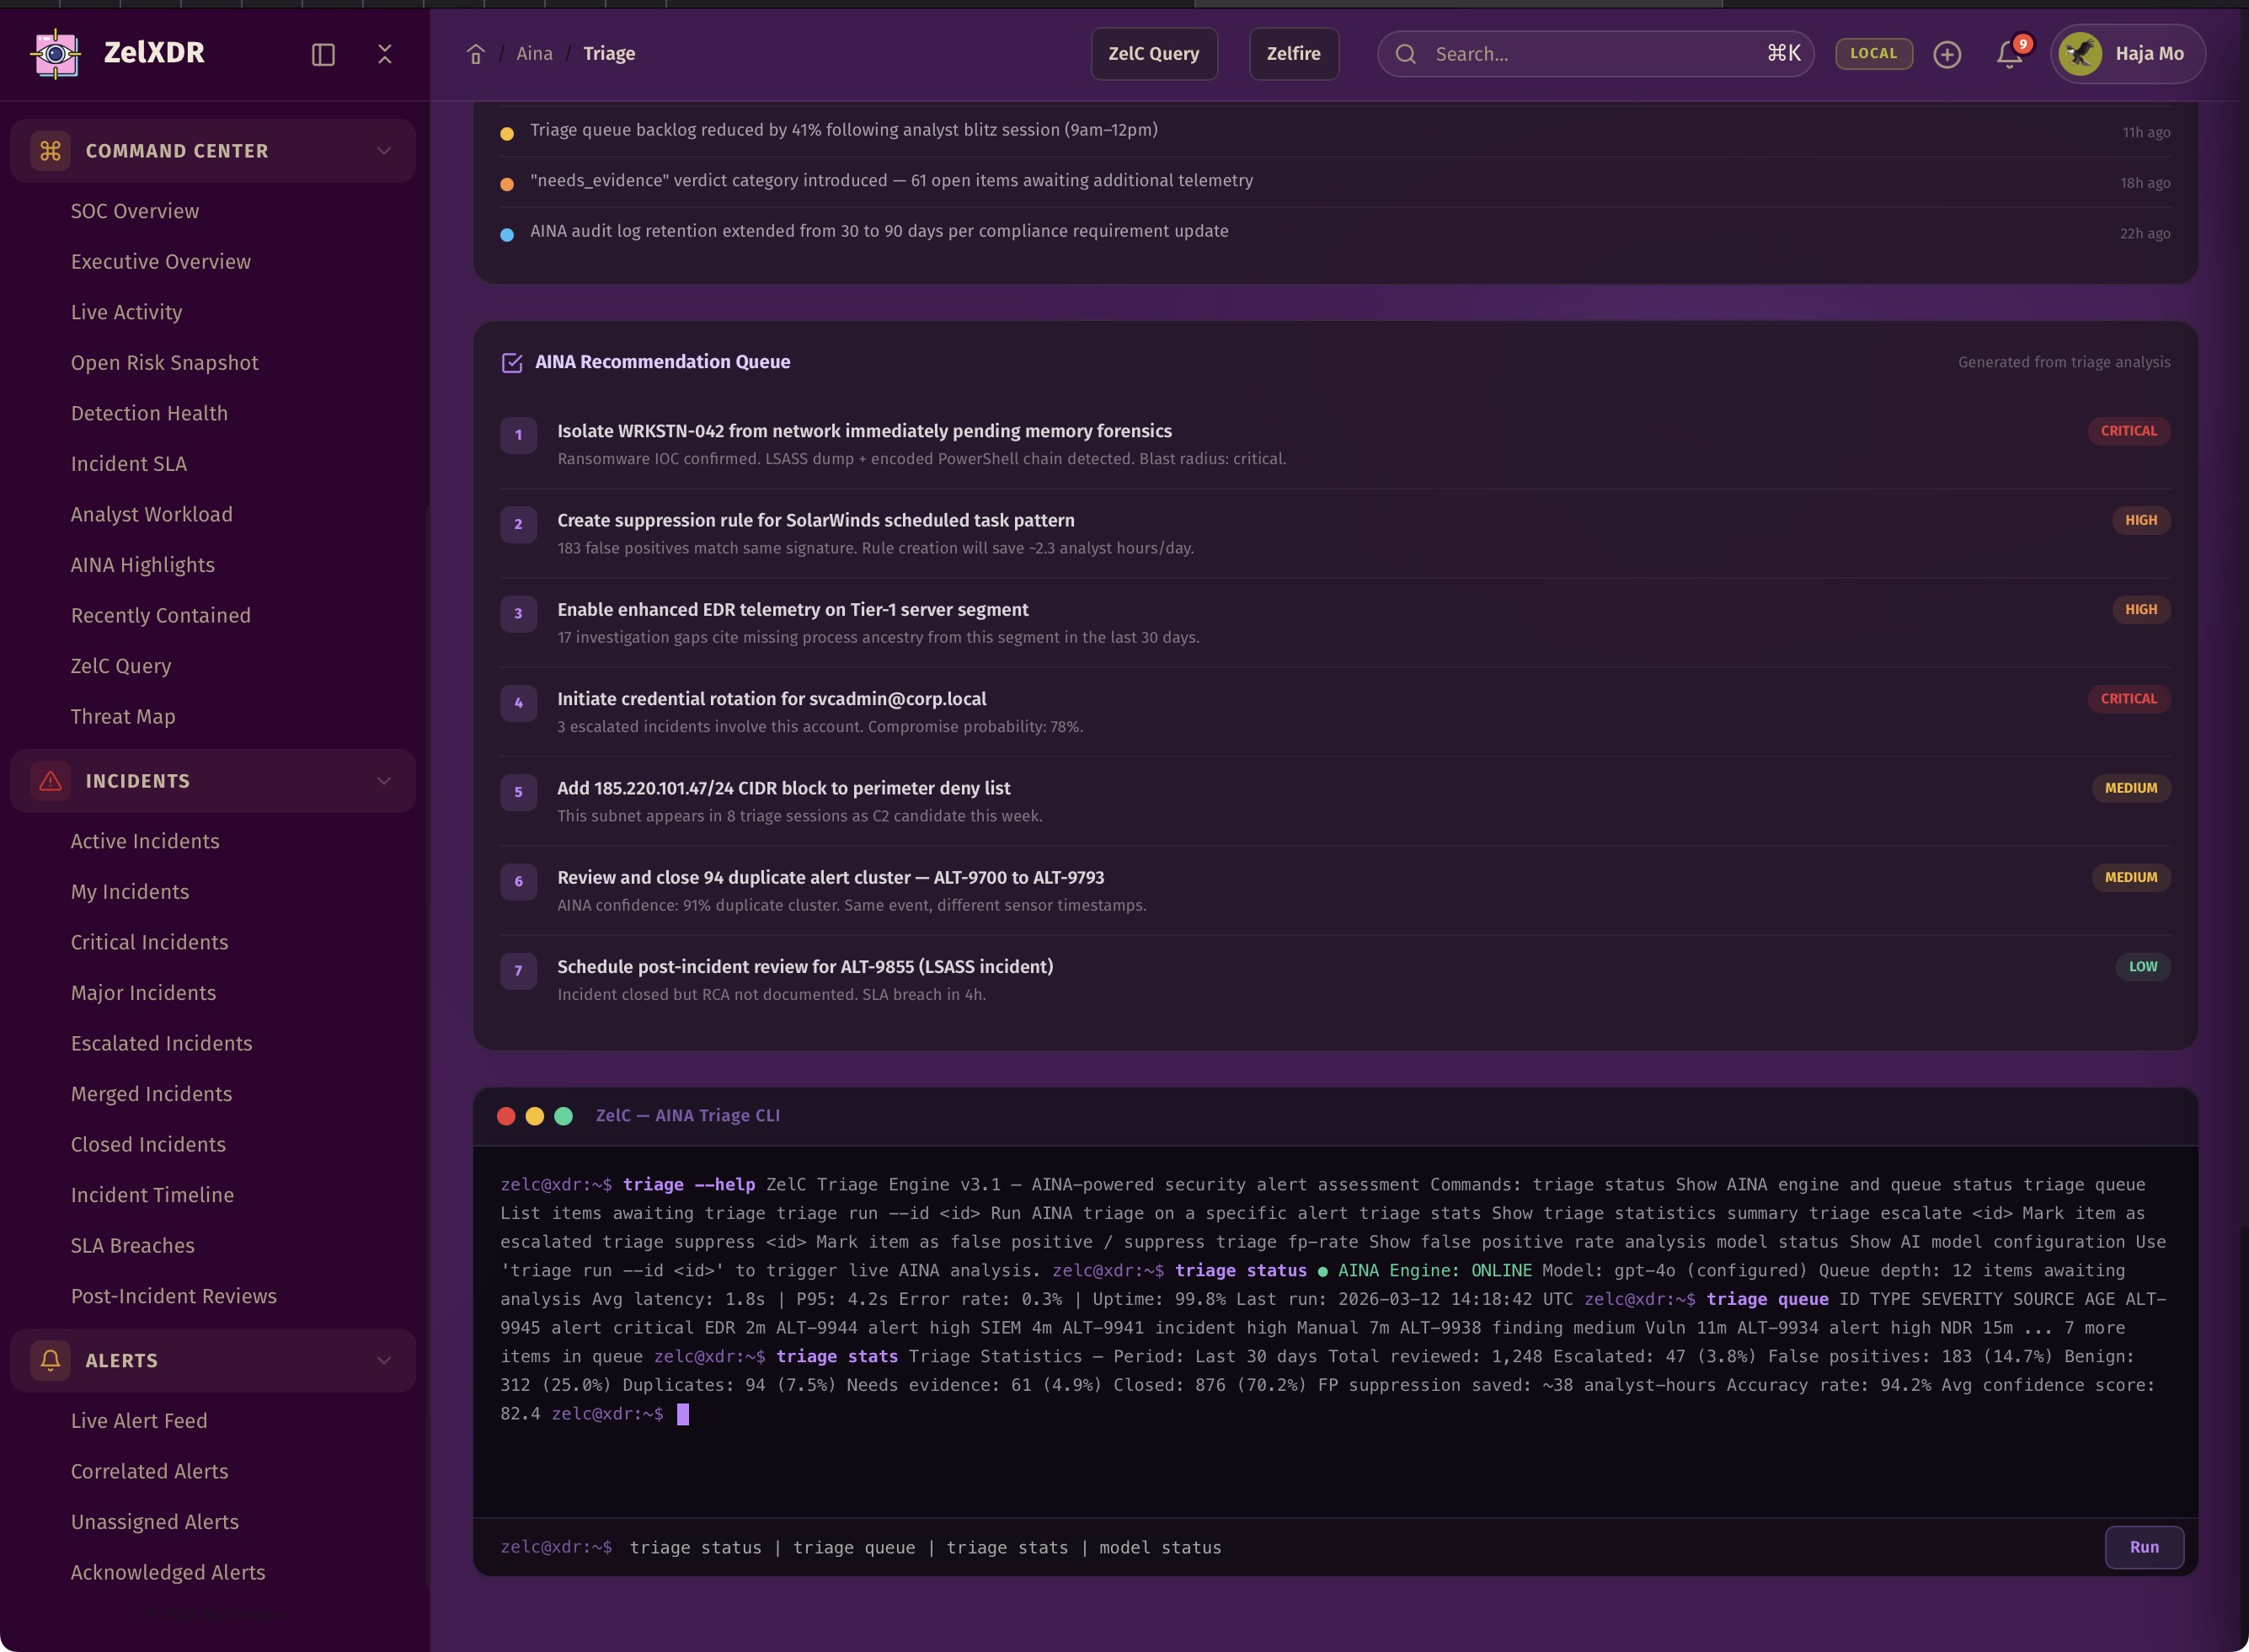
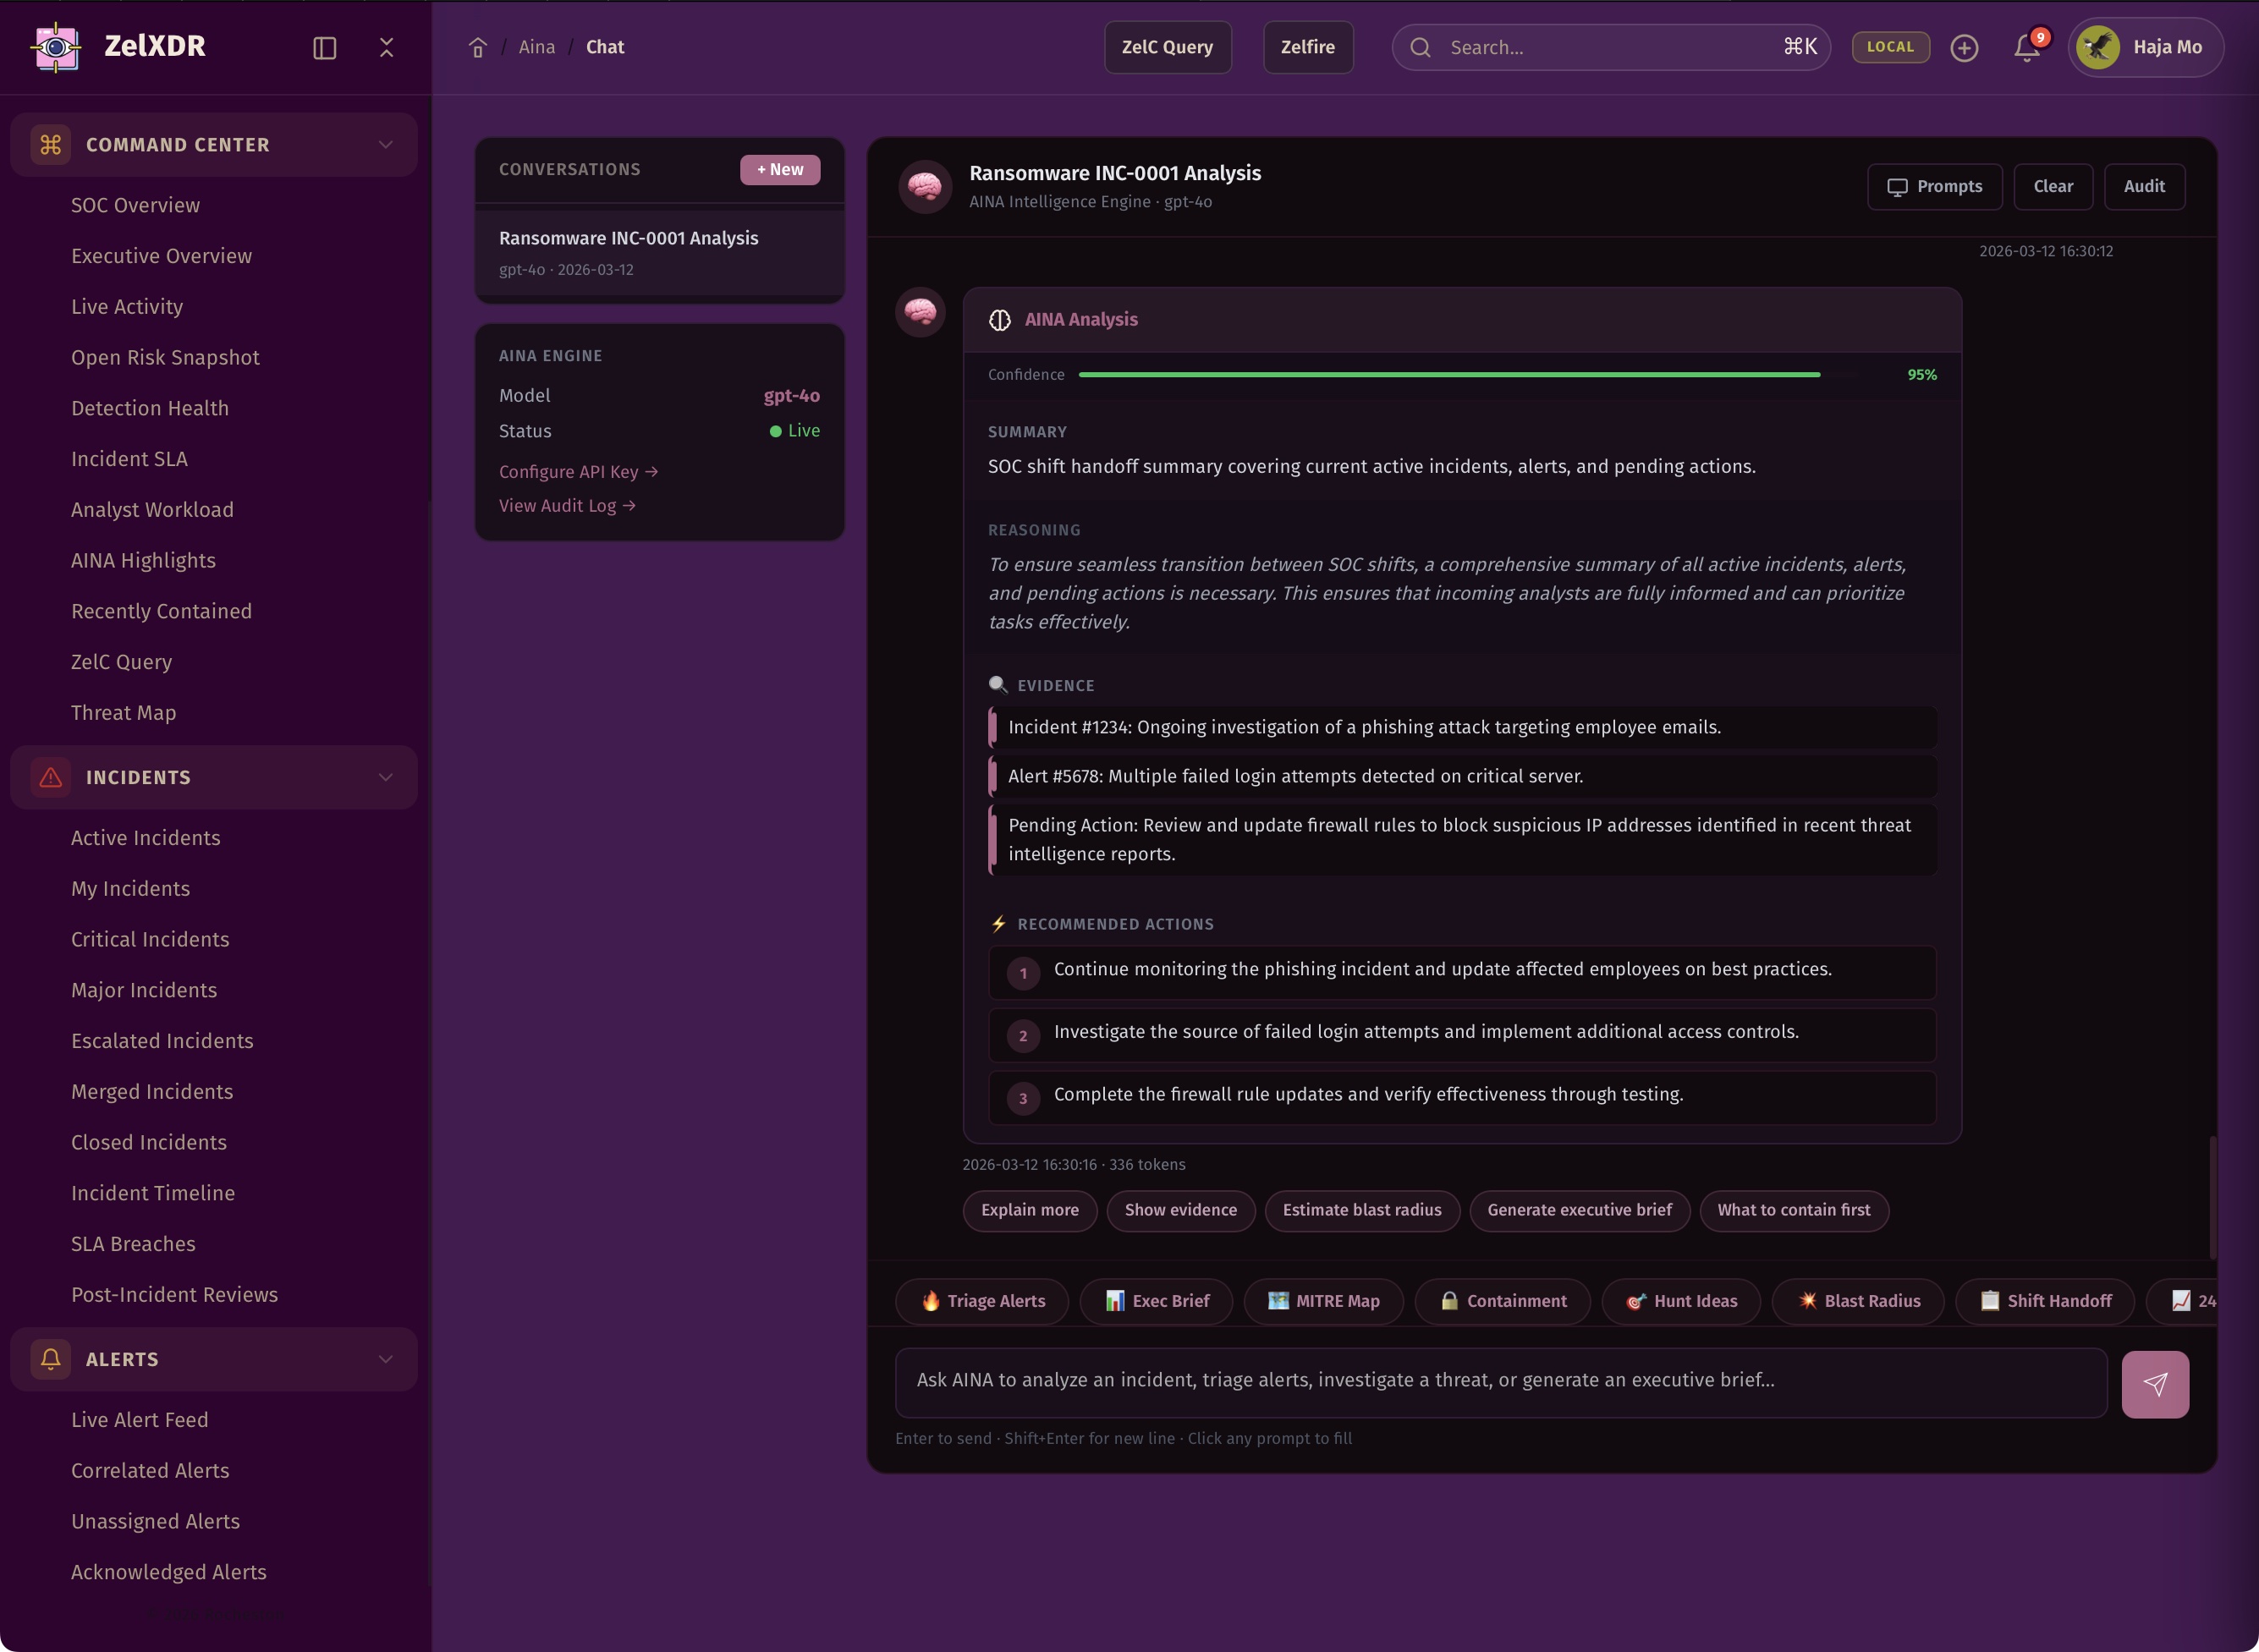
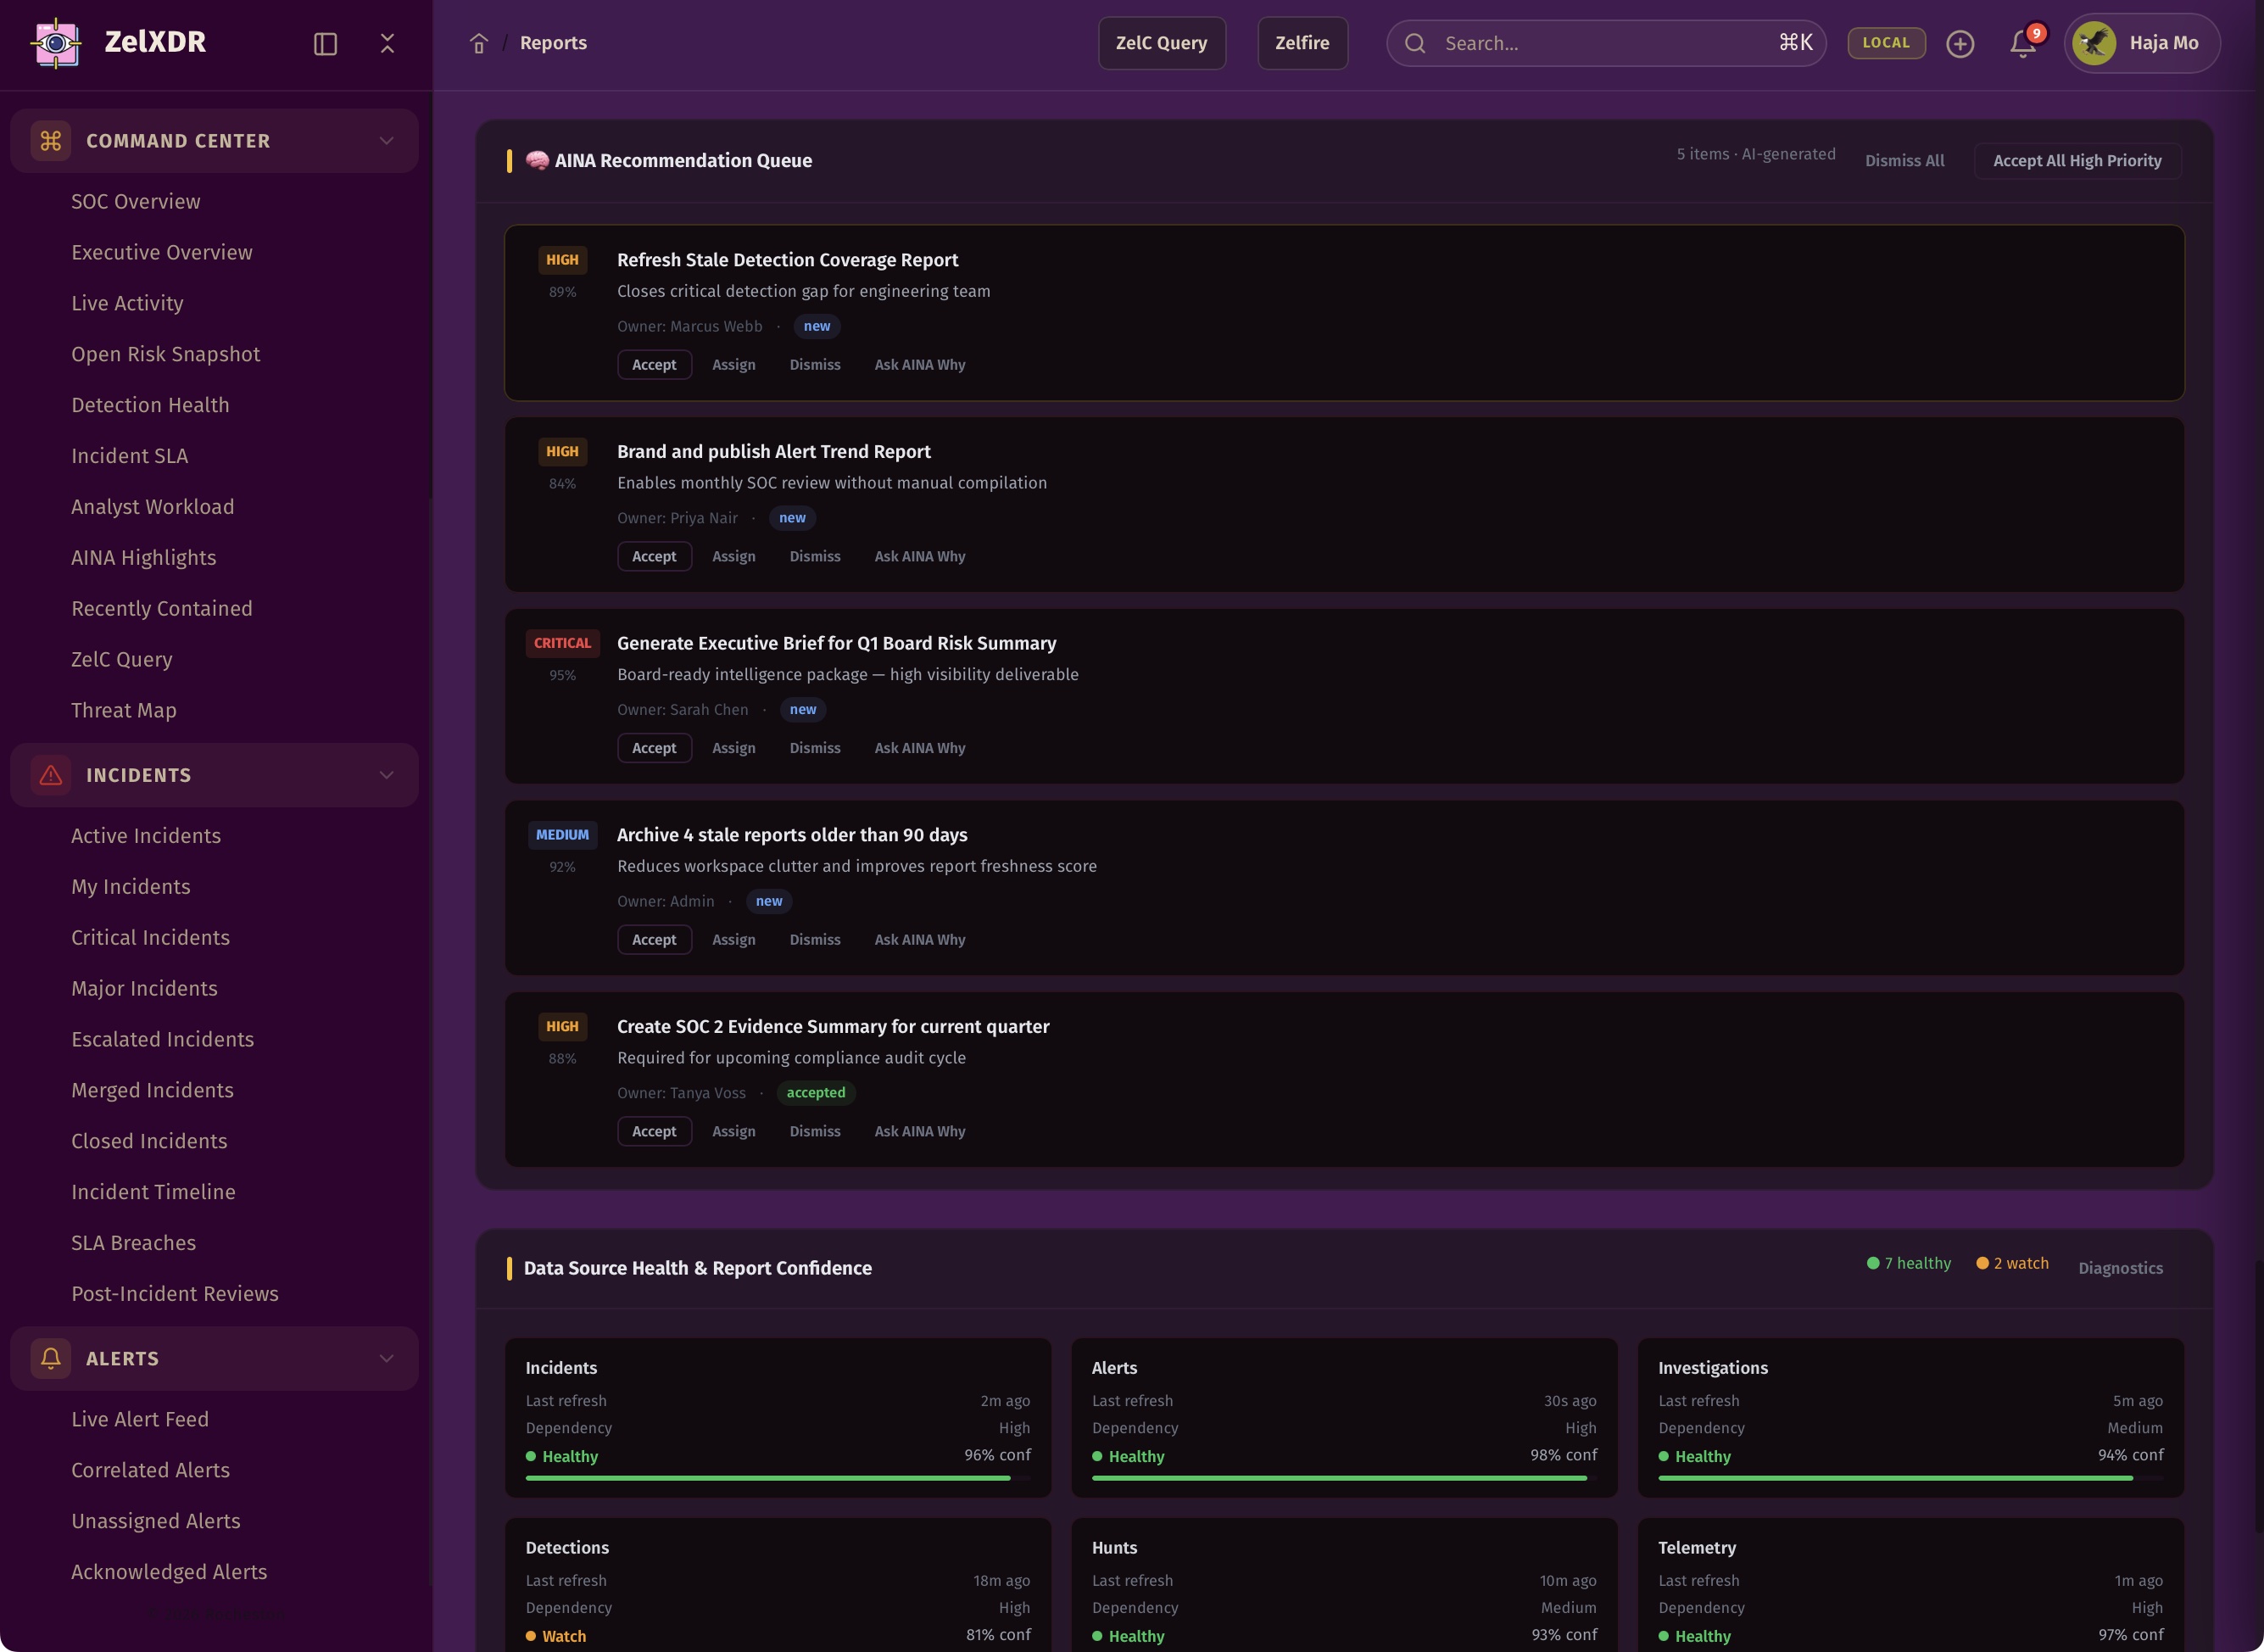
AINA helps analysts move faster by summarizing alerts, reducing noise, clustering related signals, and recommending next steps. It transforms triage from guesswork into guided security decision-making.
AINA turns alert overload into analyst clarity.
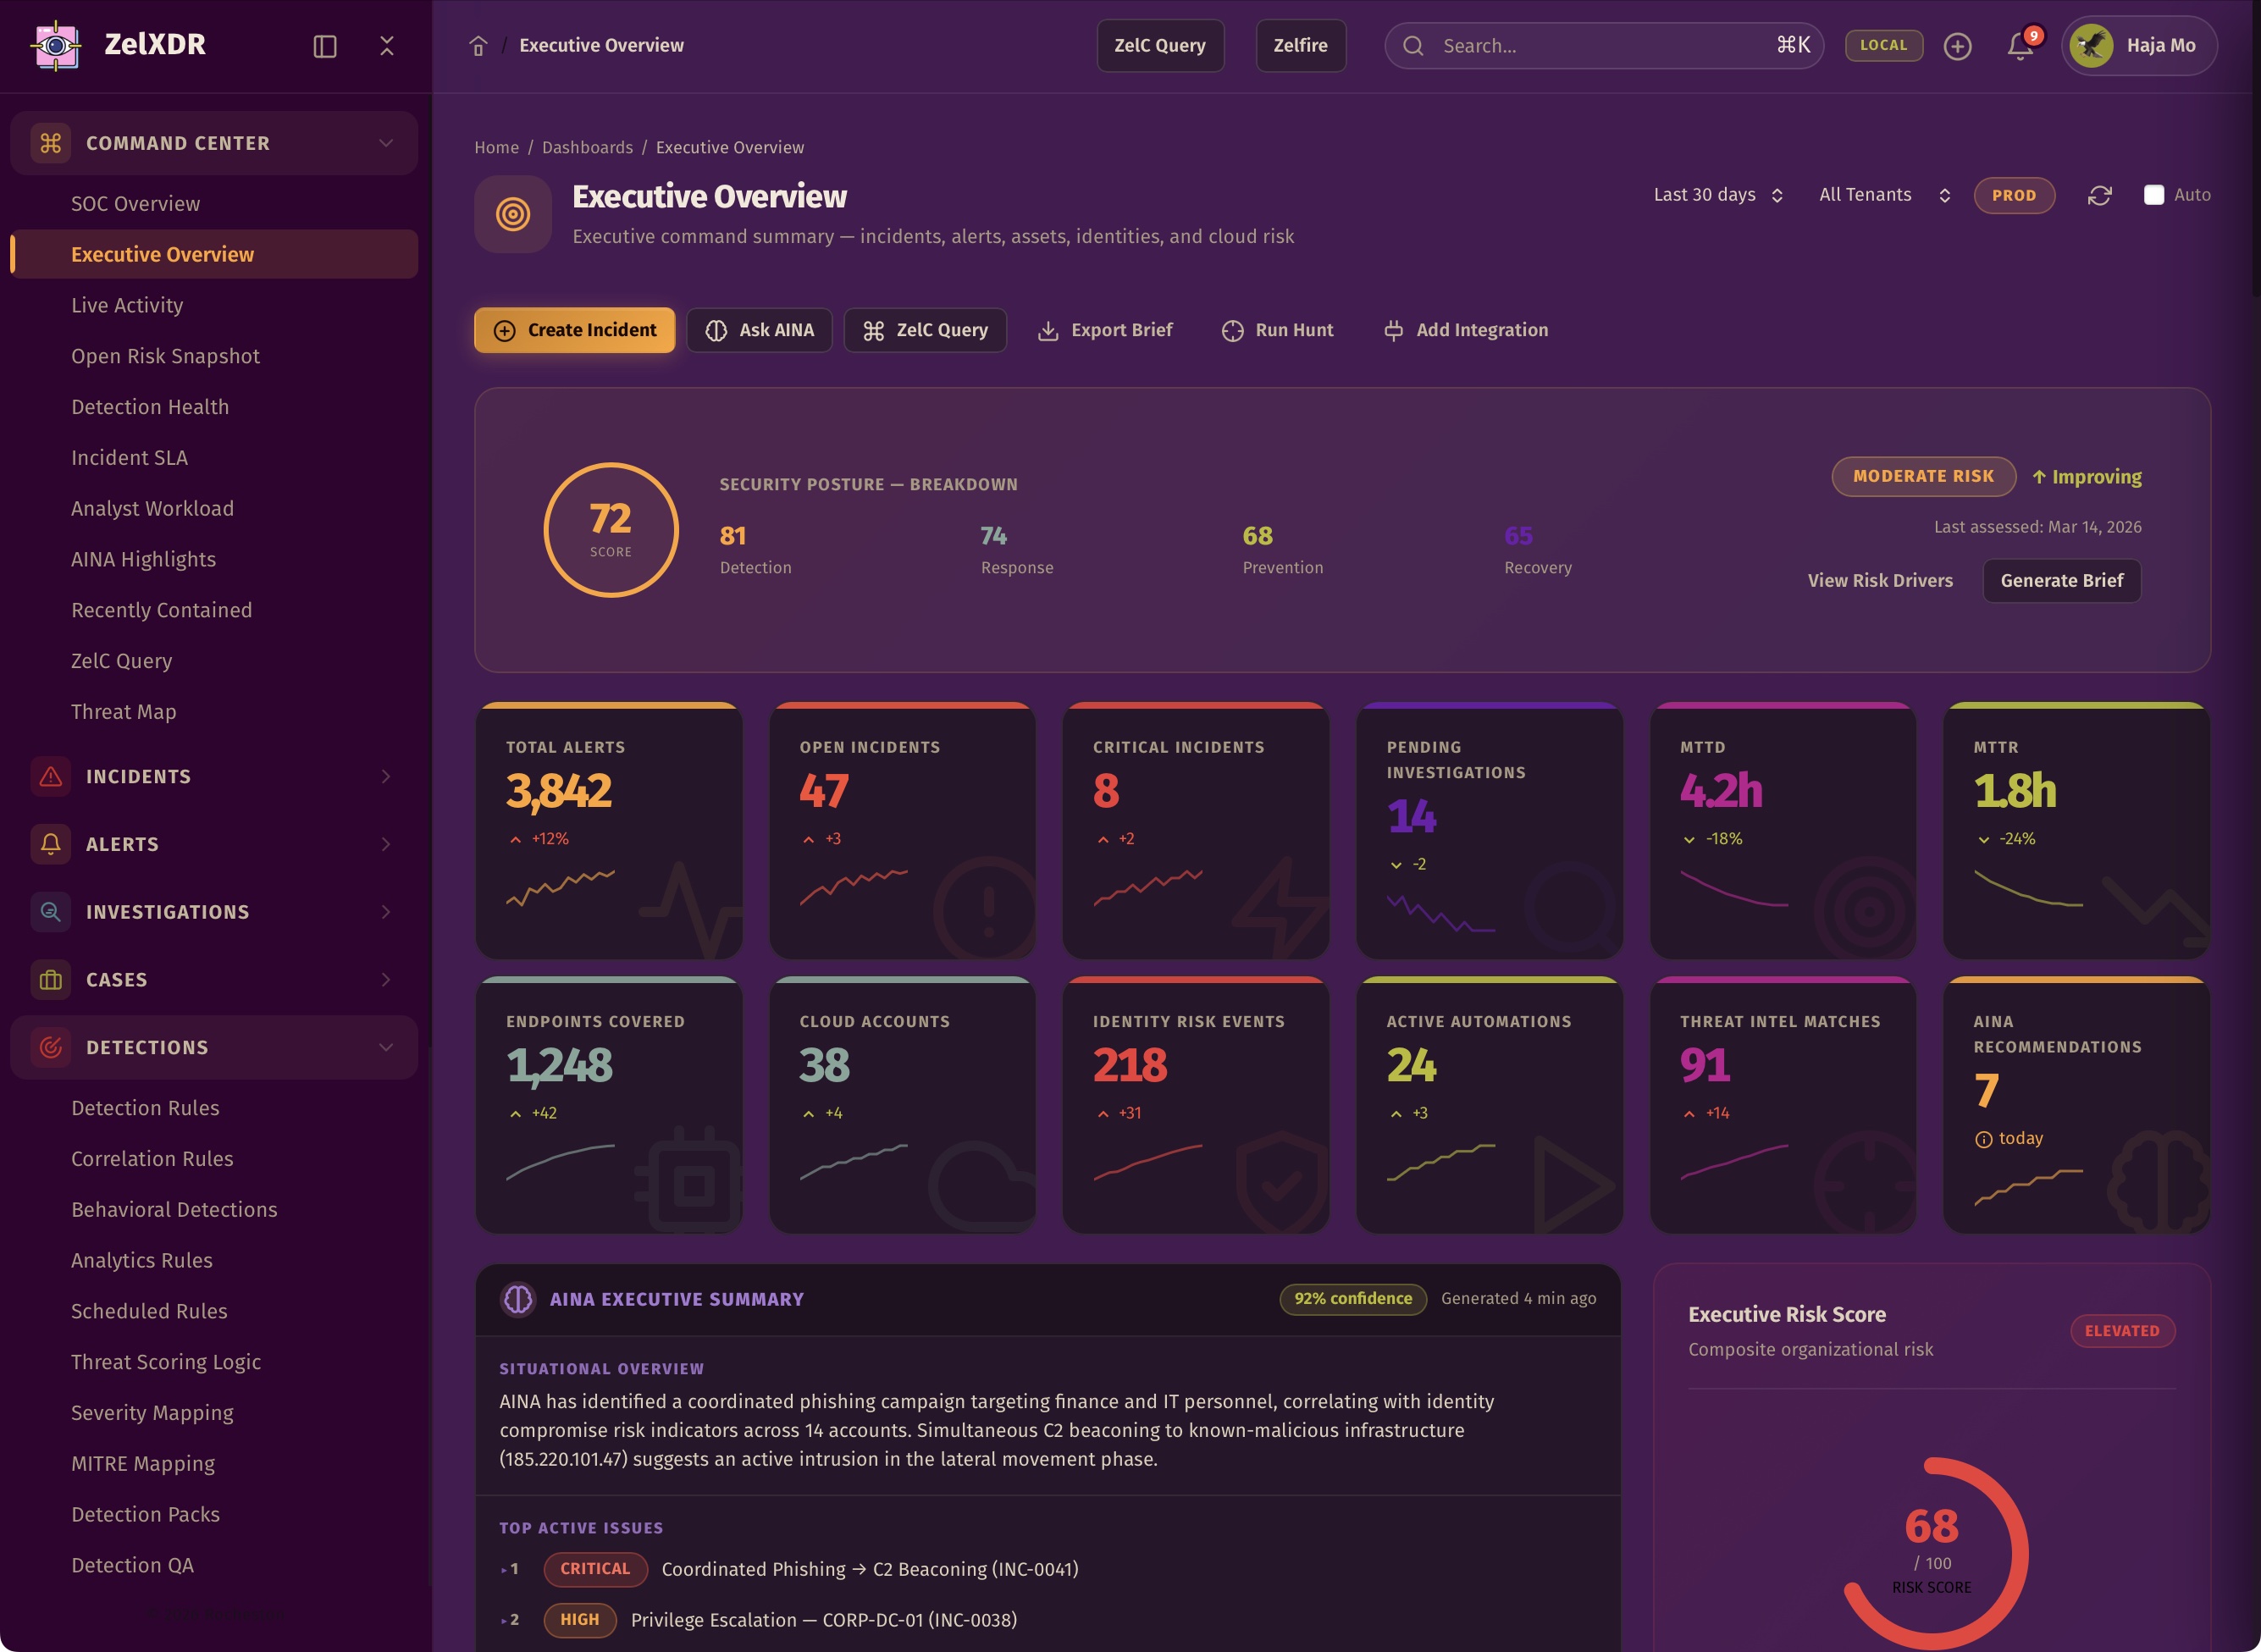
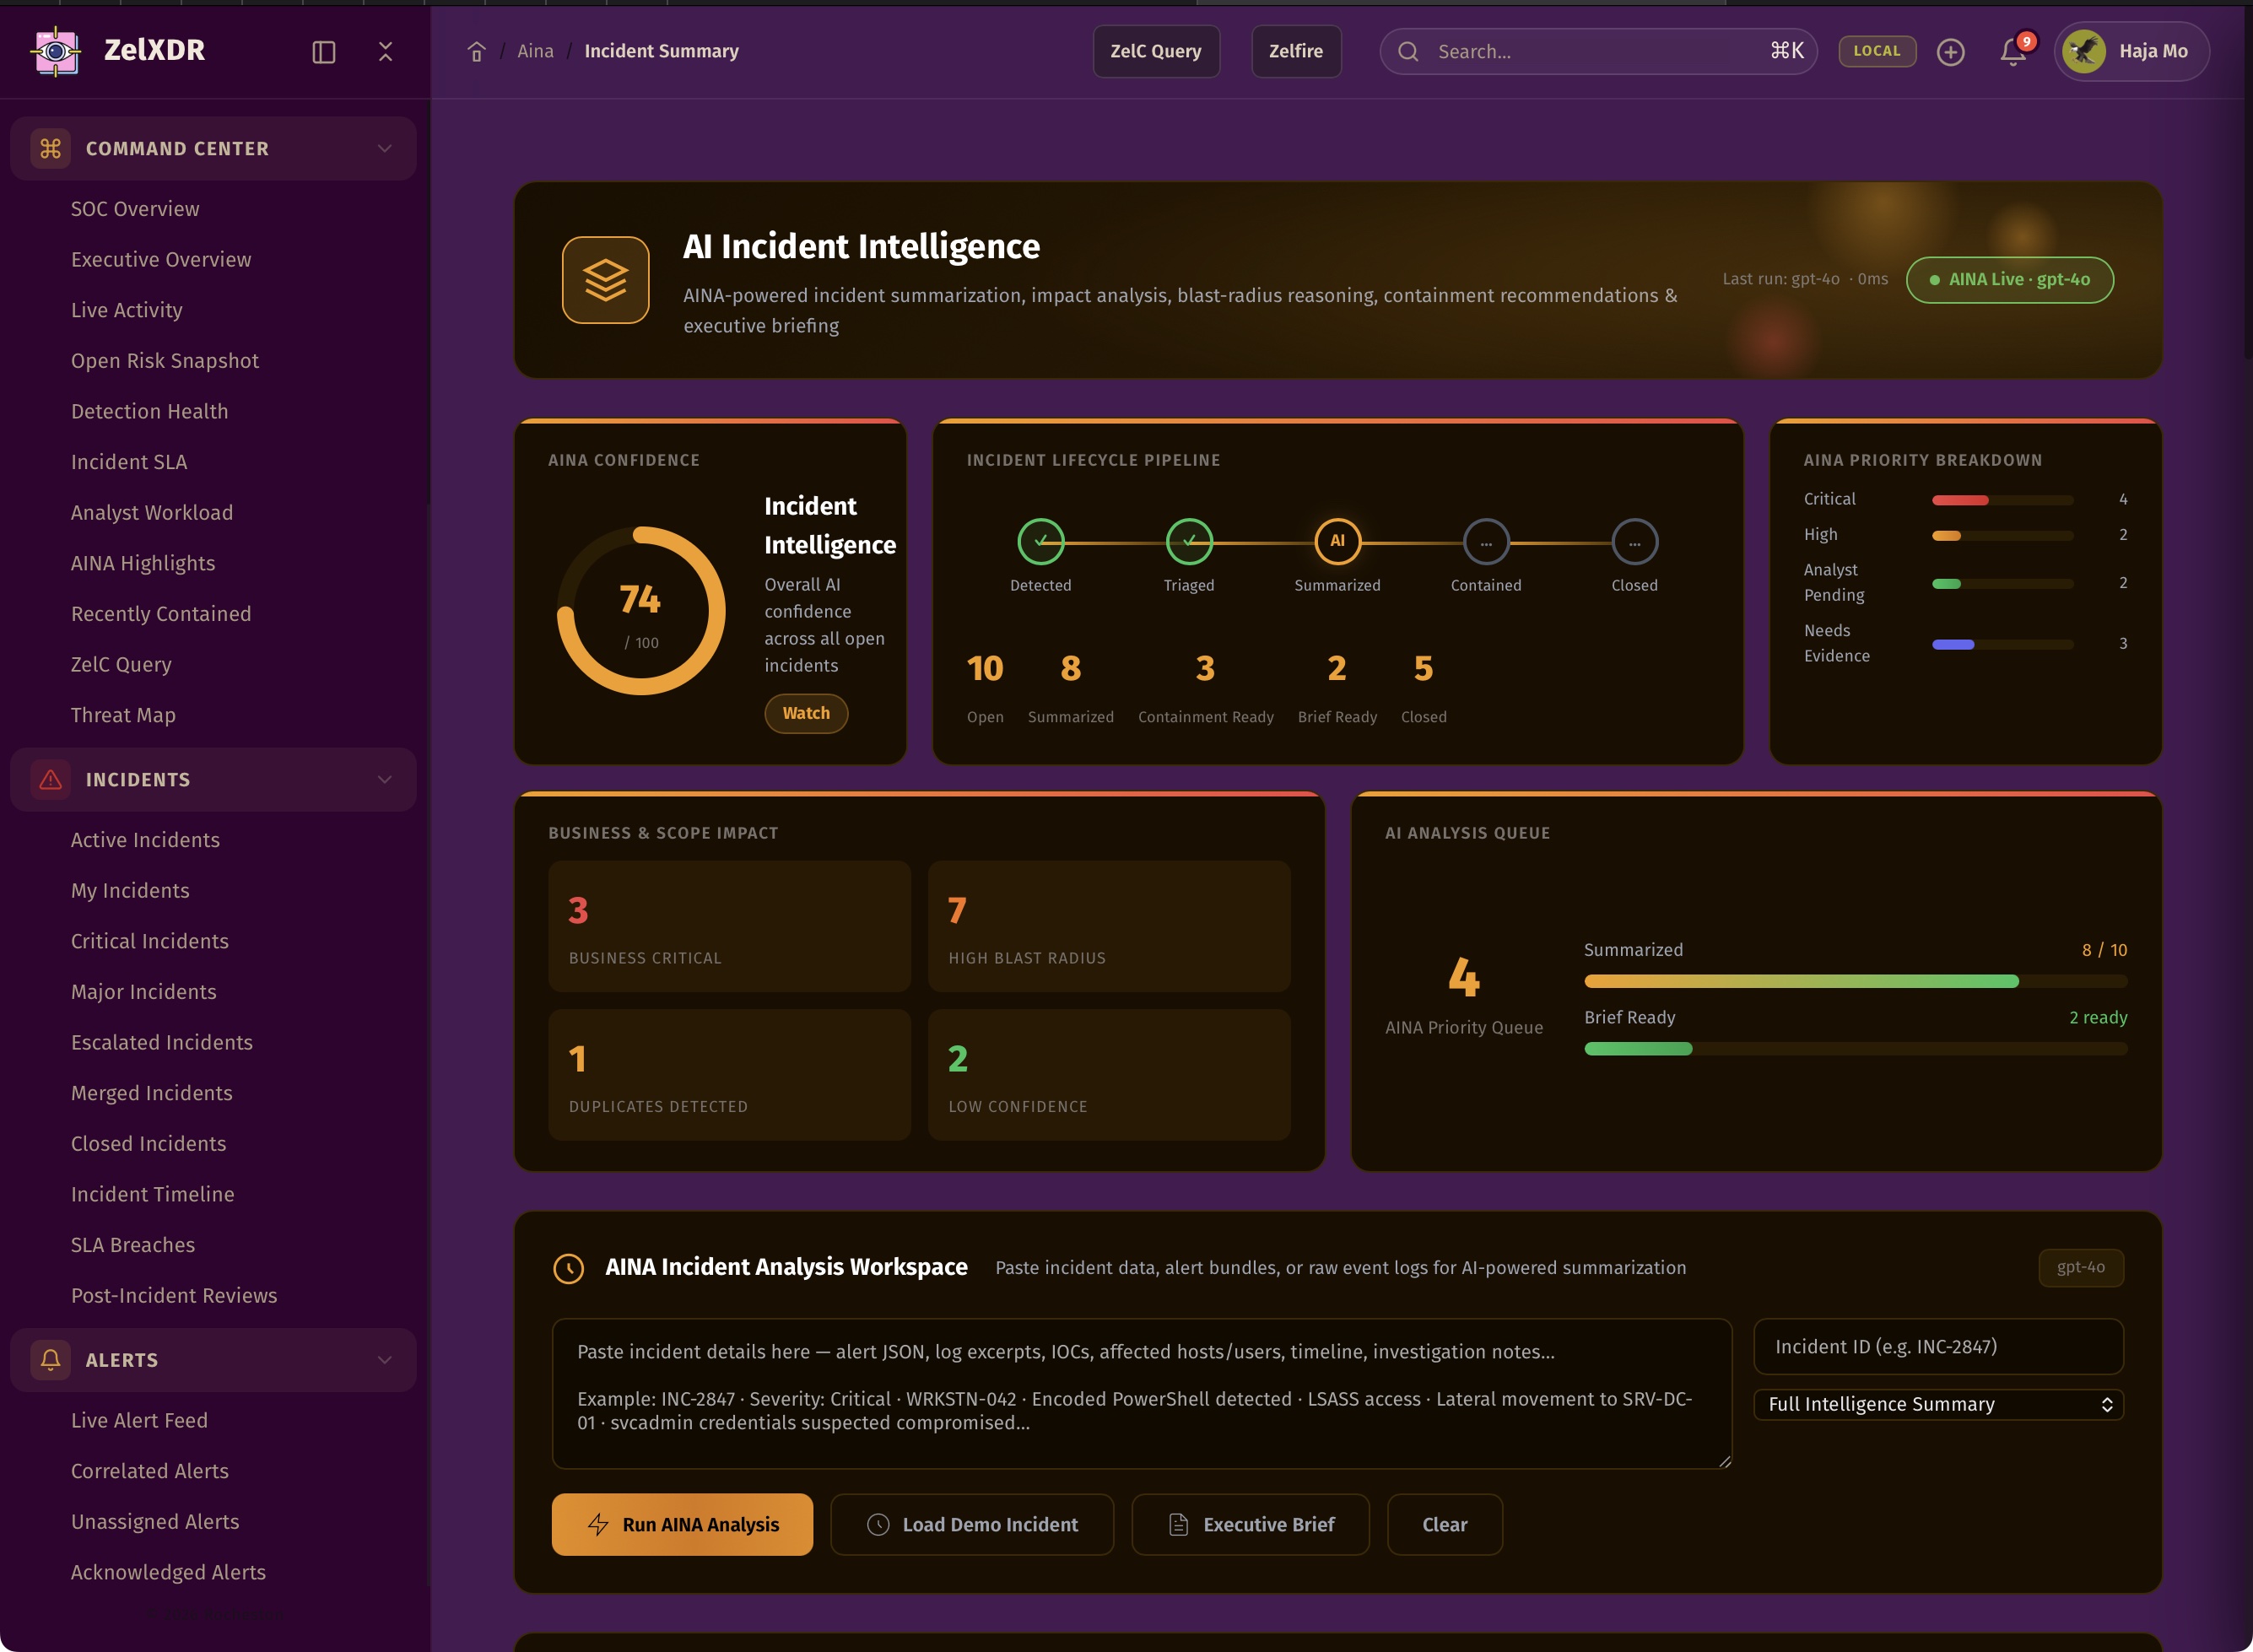
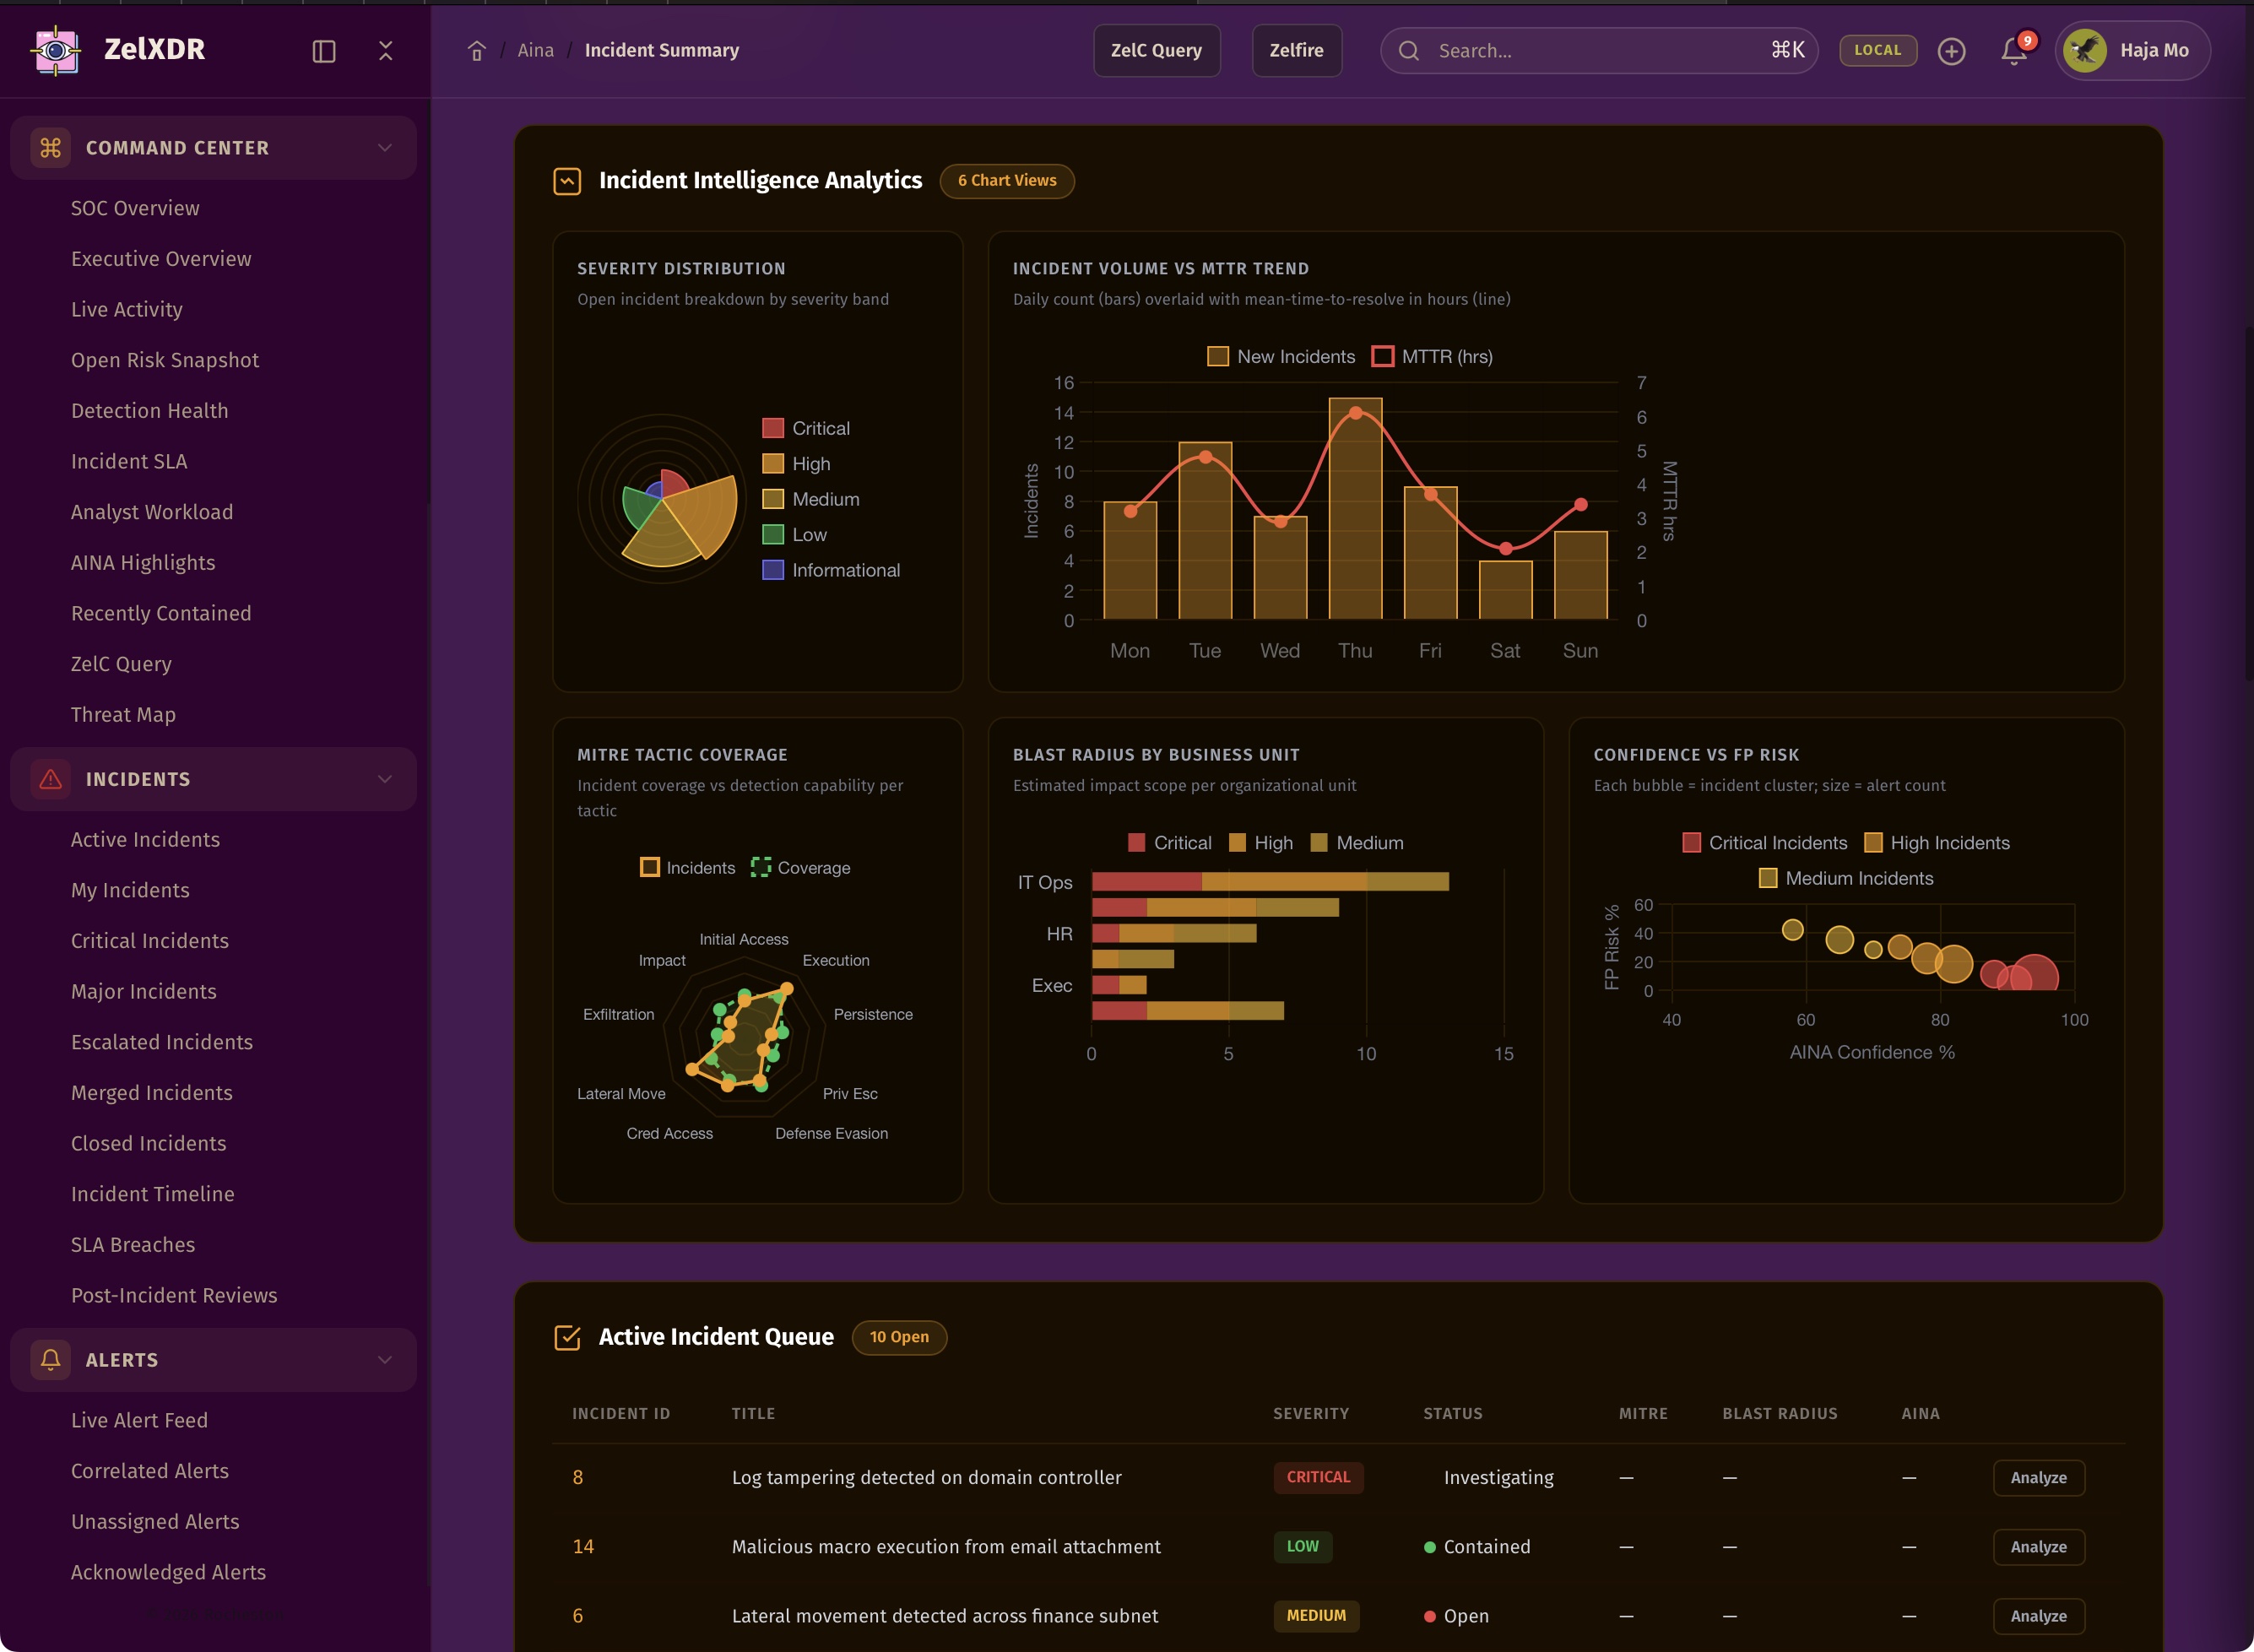
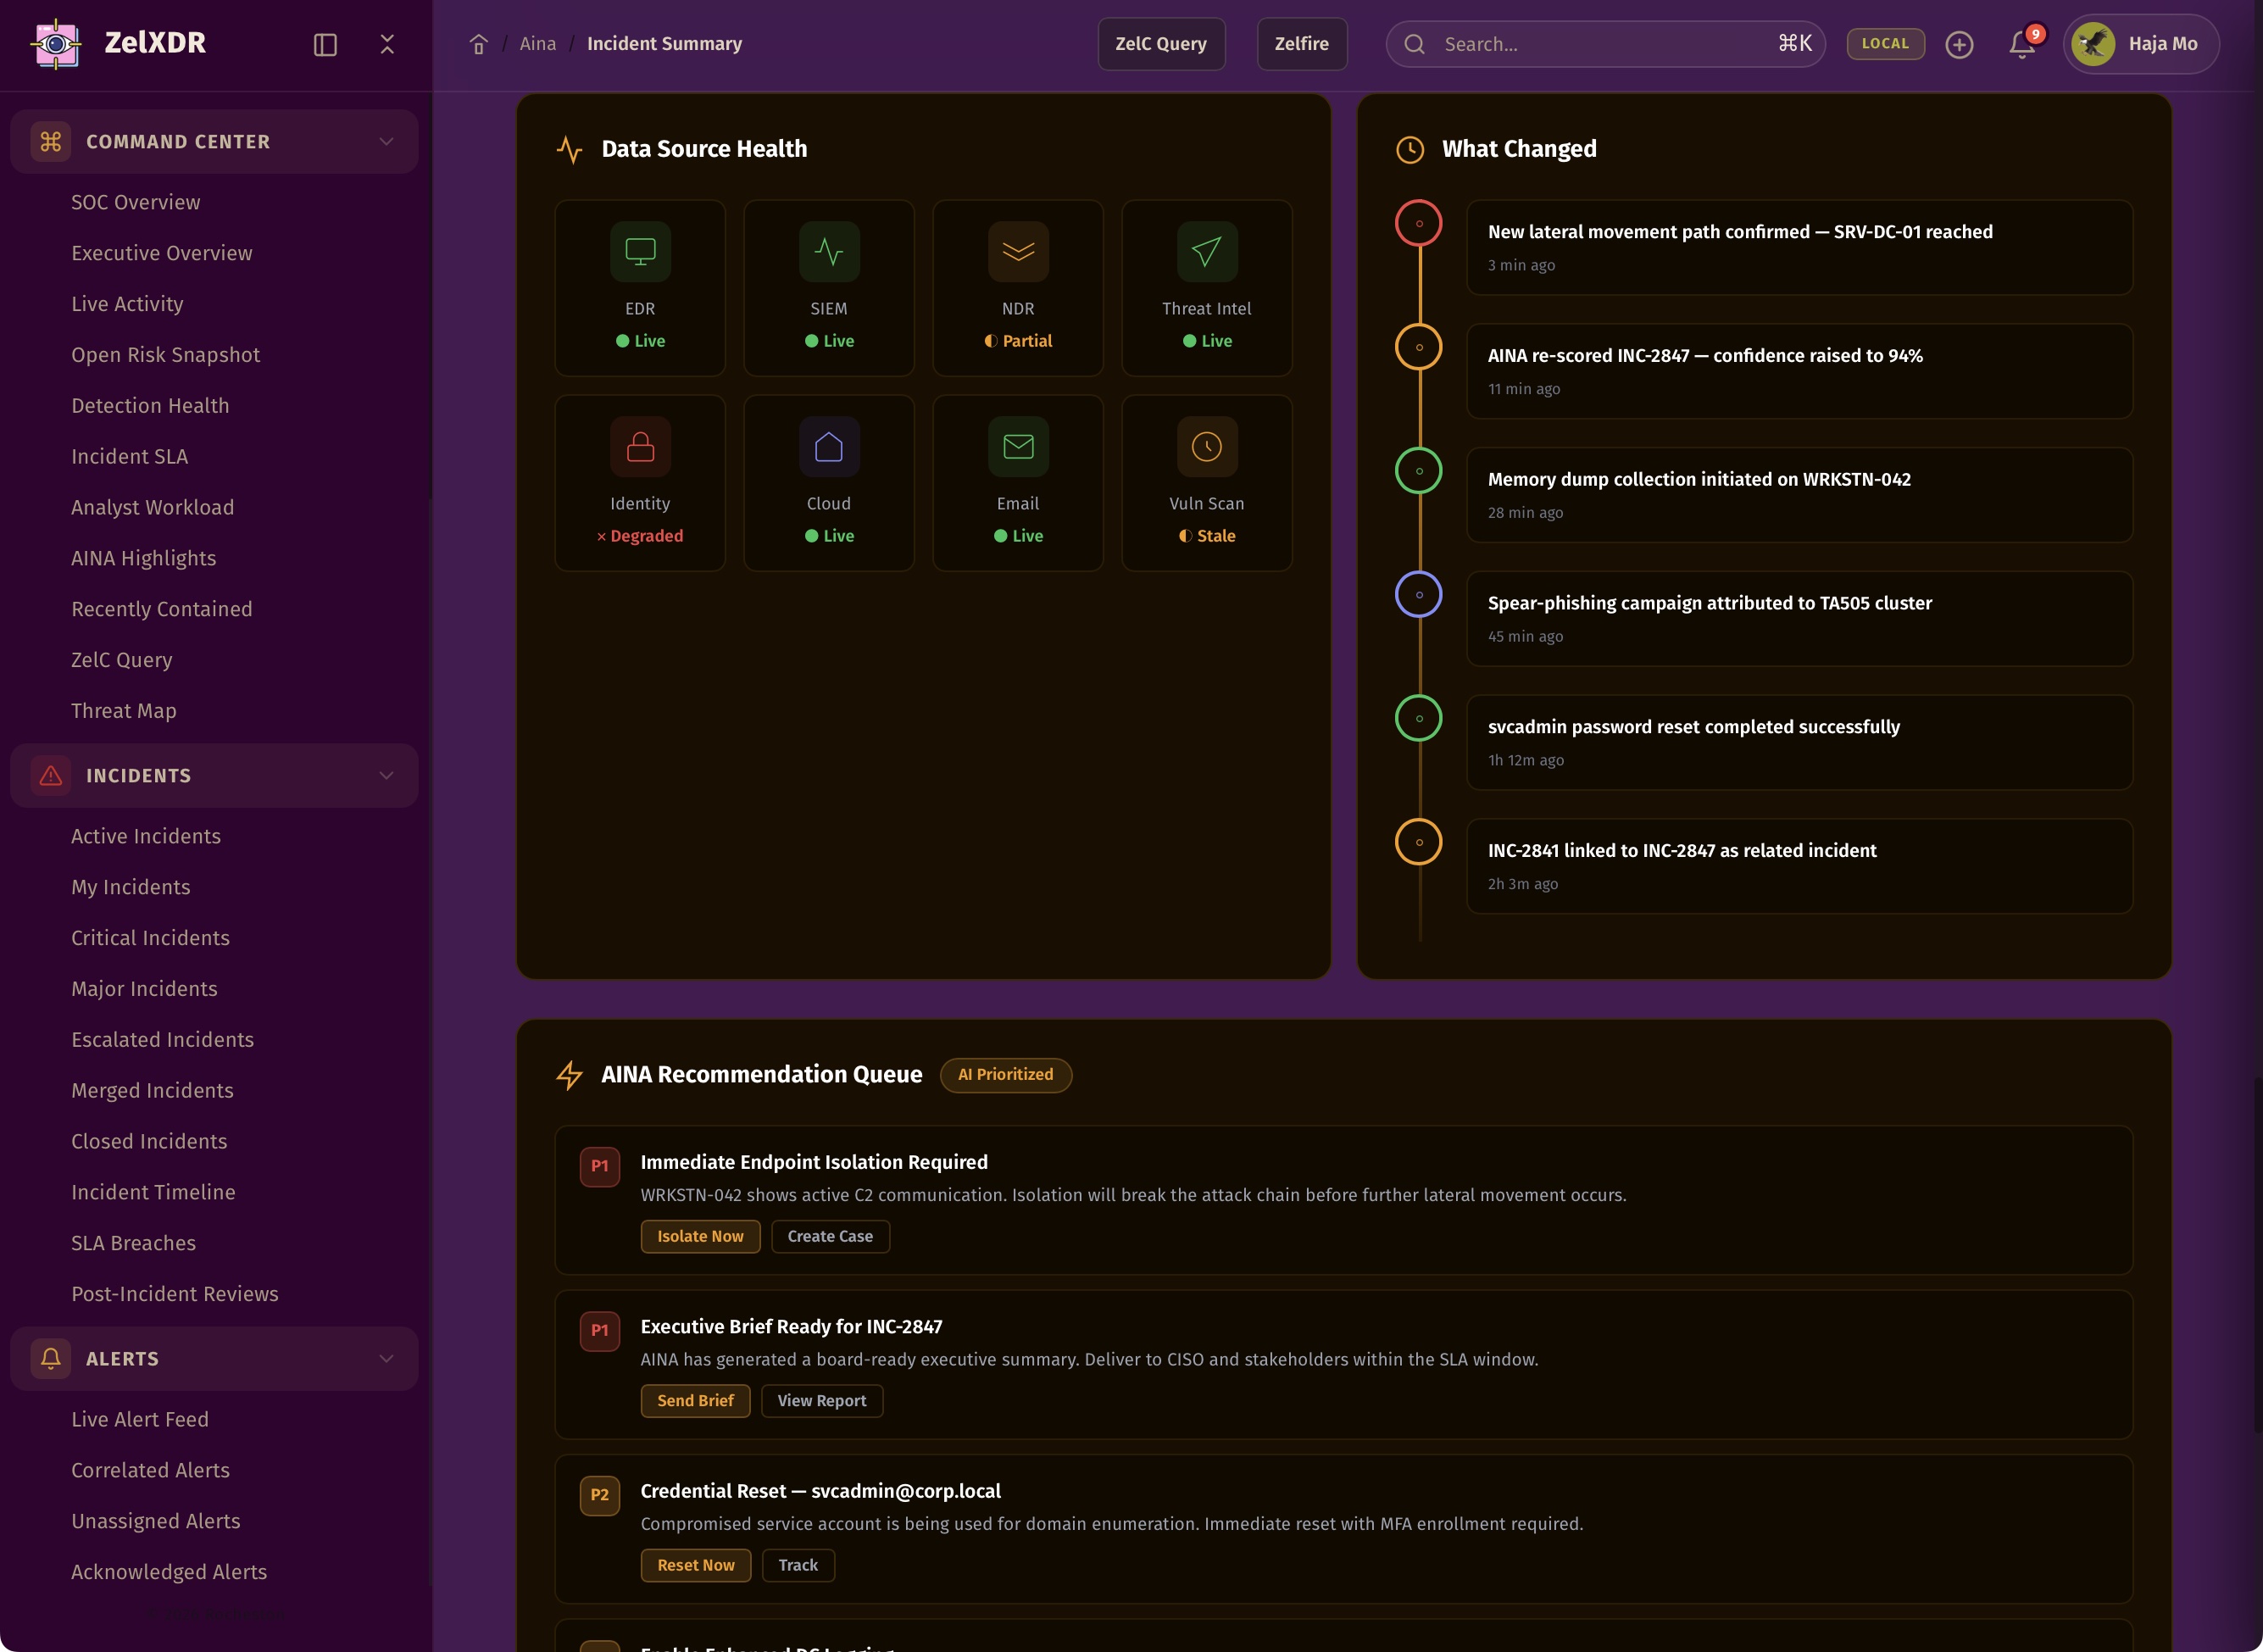
ZelXDR uses AINA to explain incidents in plain English, estimate likely root cause, outline blast radius, and recommend containment actions. It helps both analysts and leadership understand what truly matters.
Incidents become clearer when intelligence explains the why.
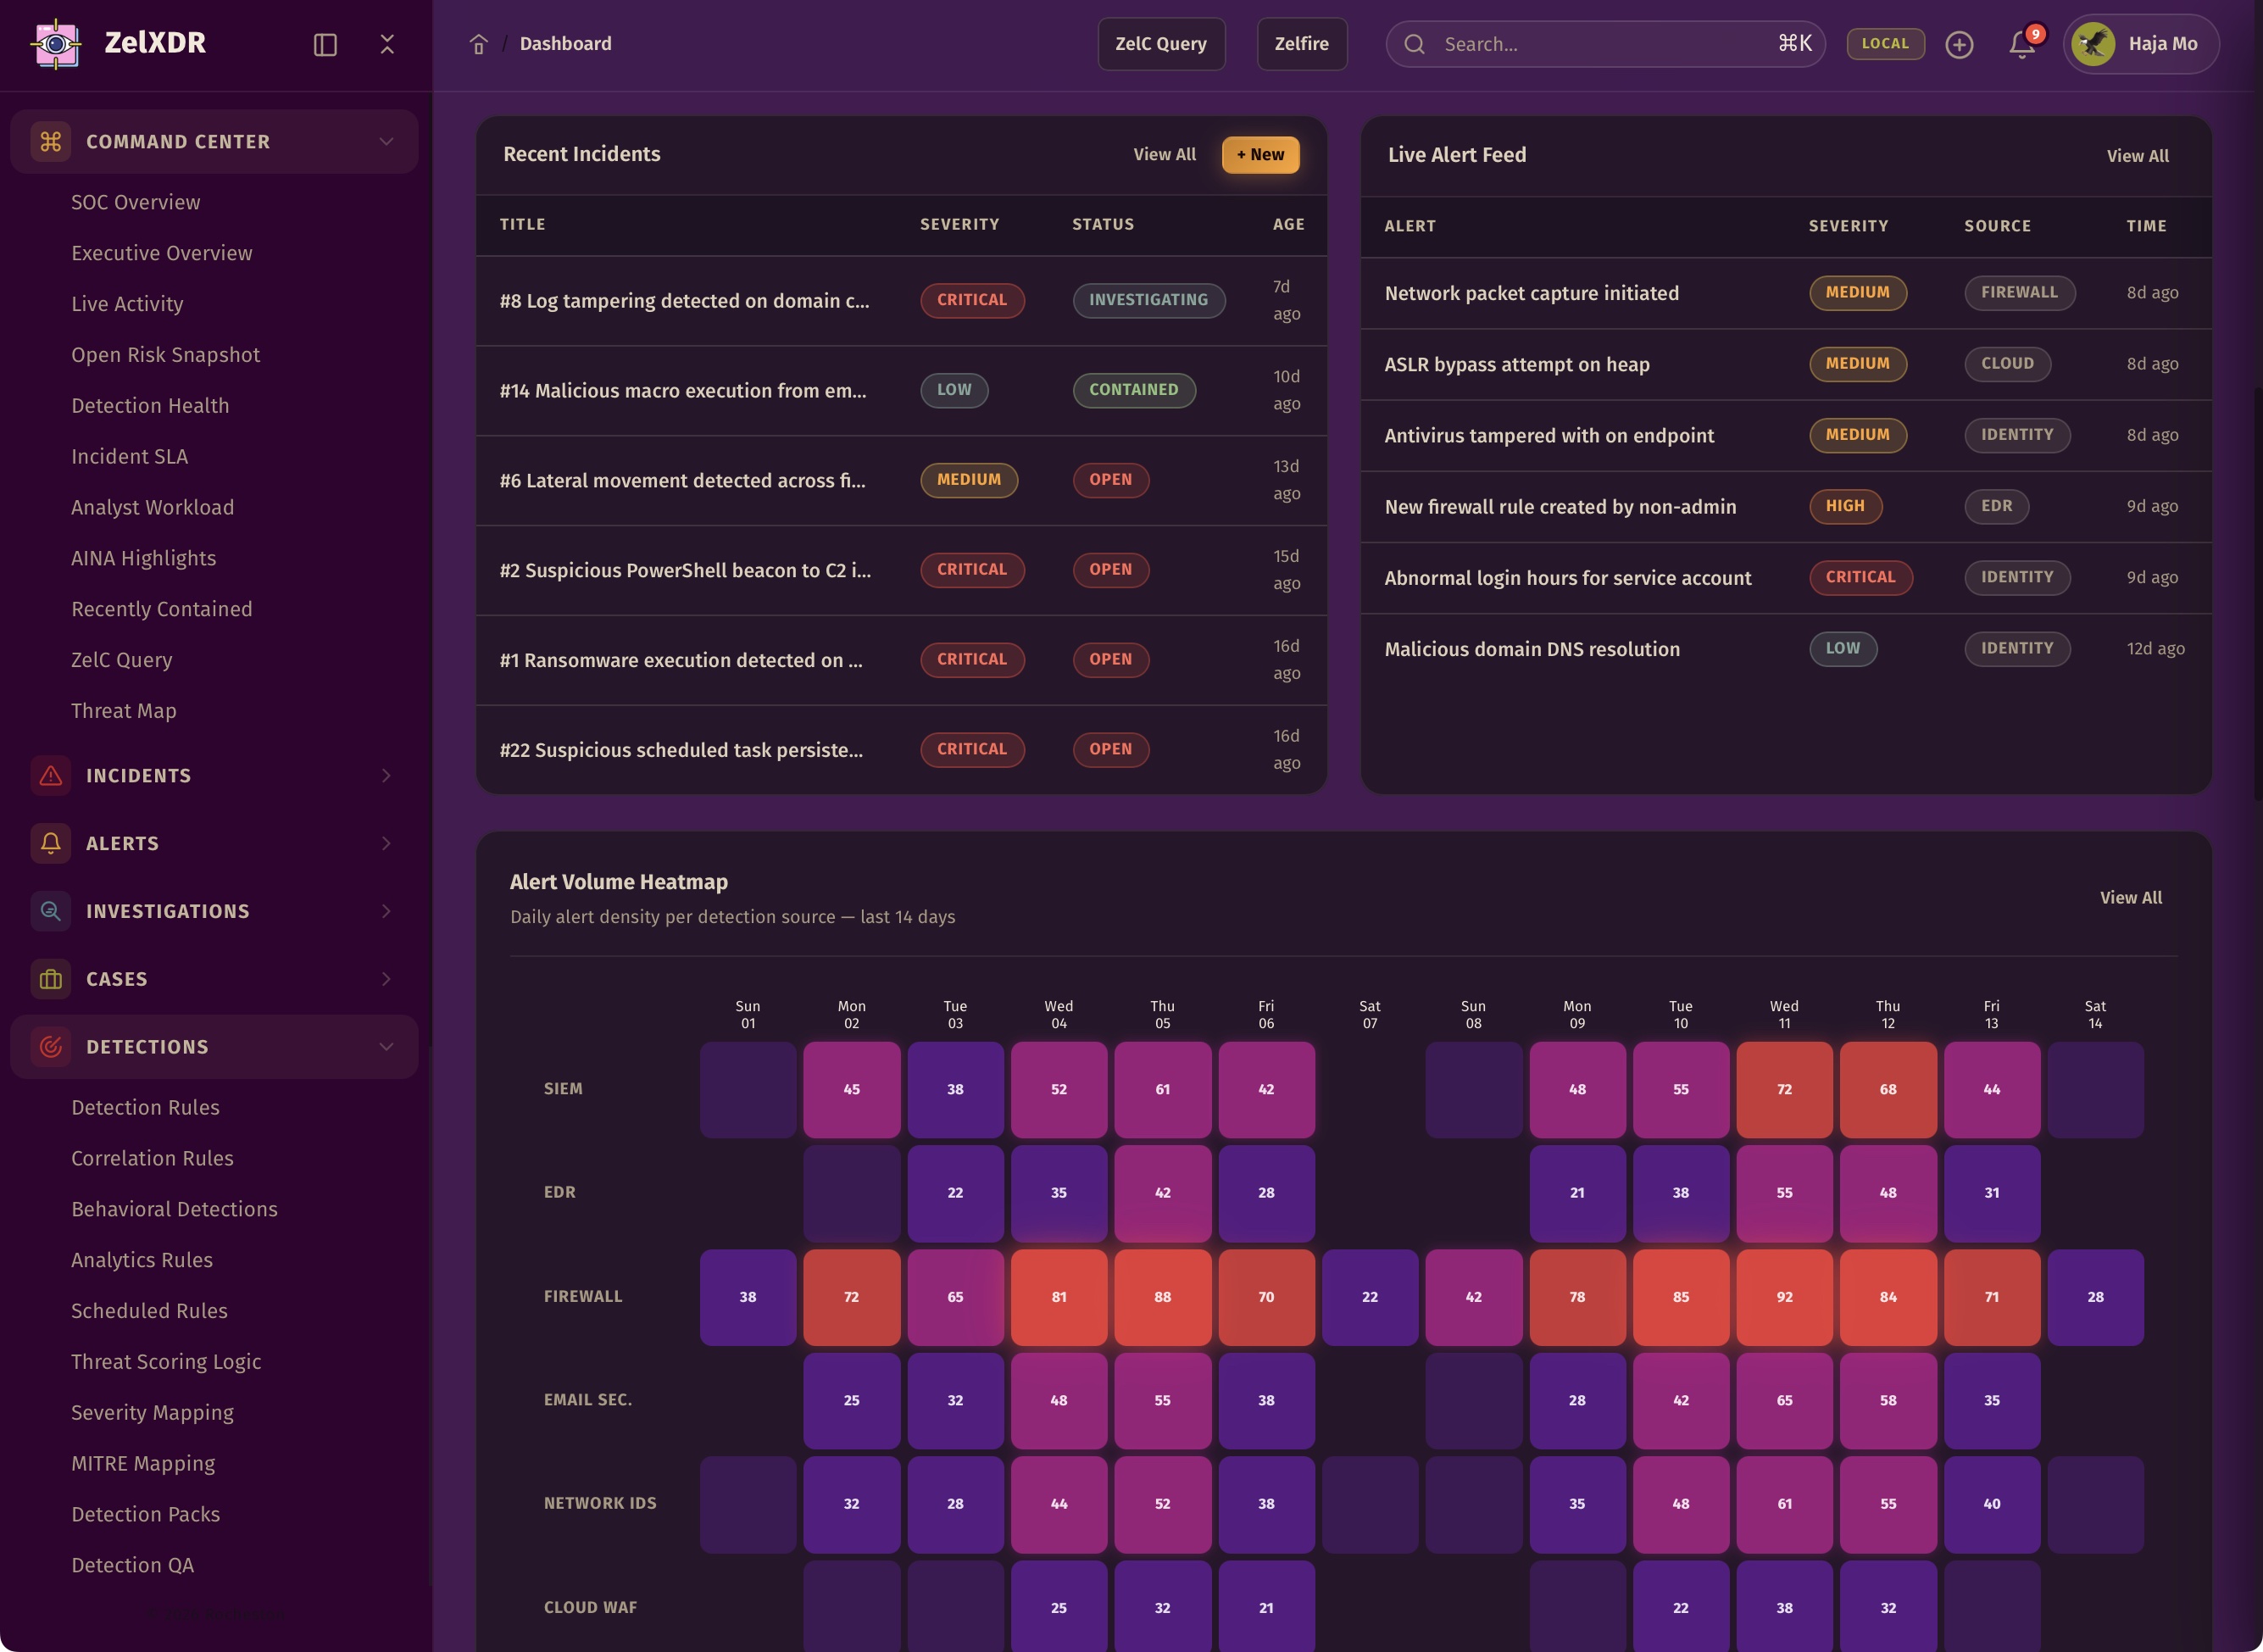
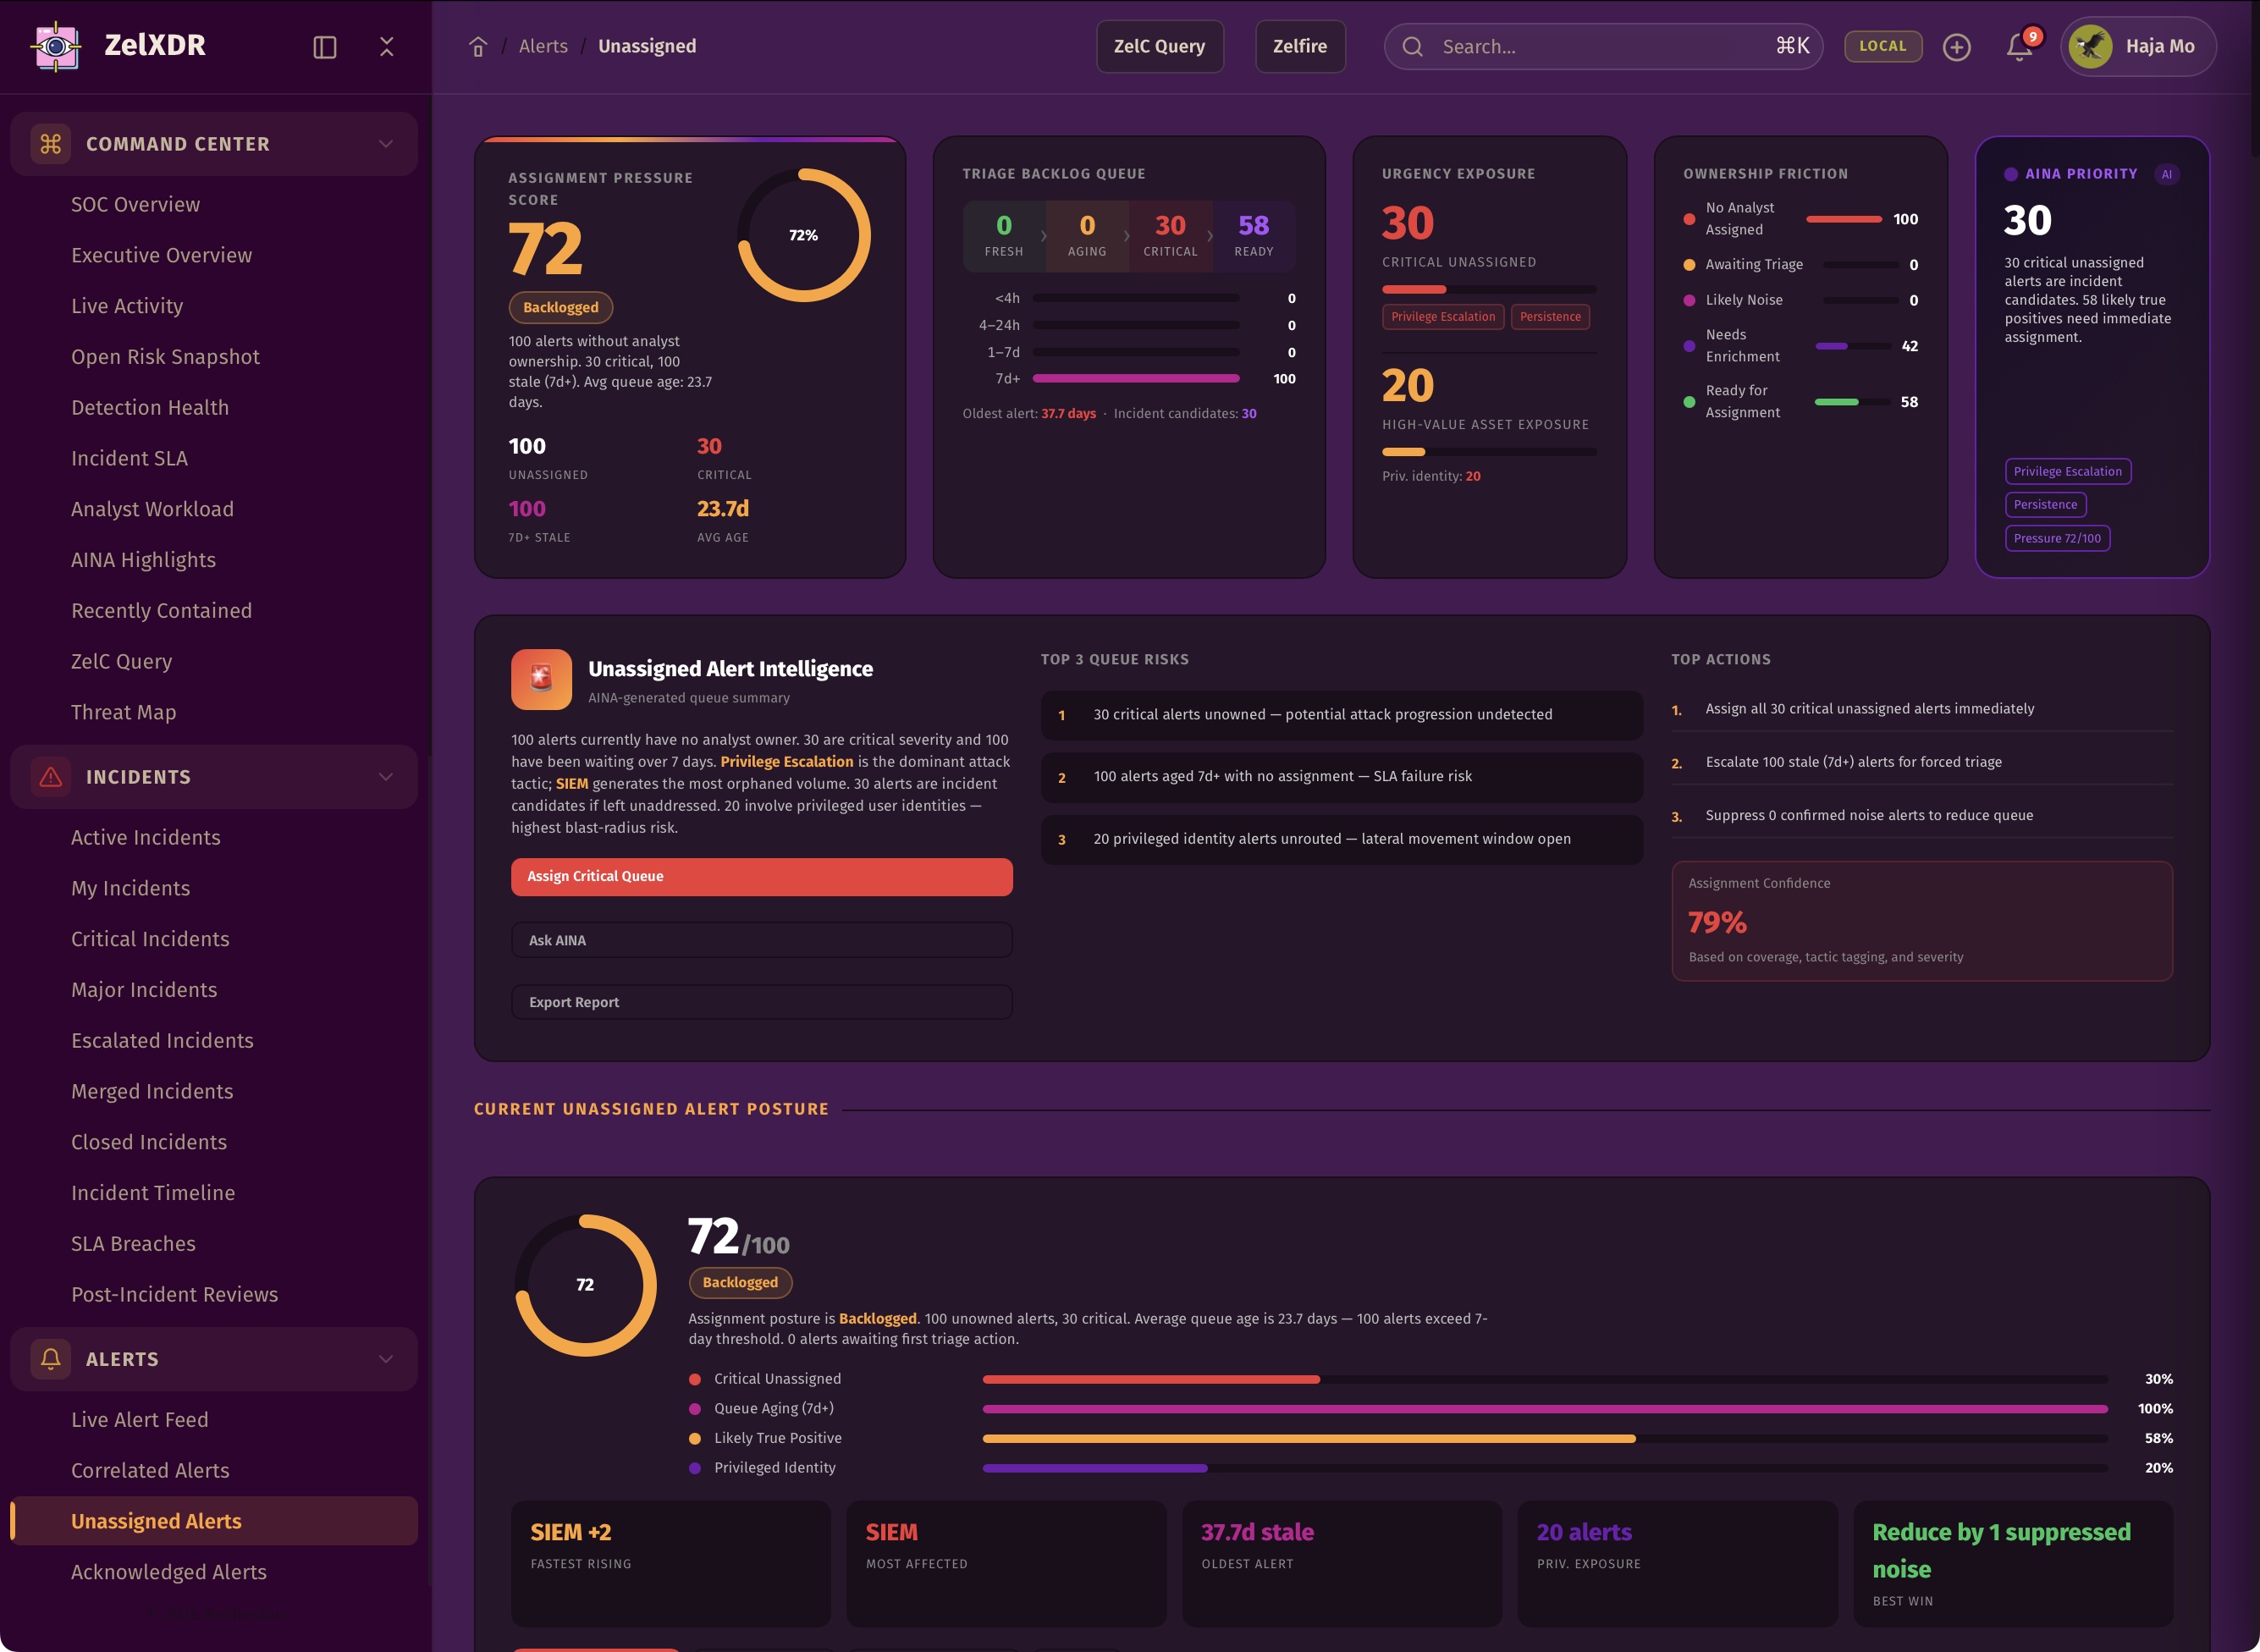
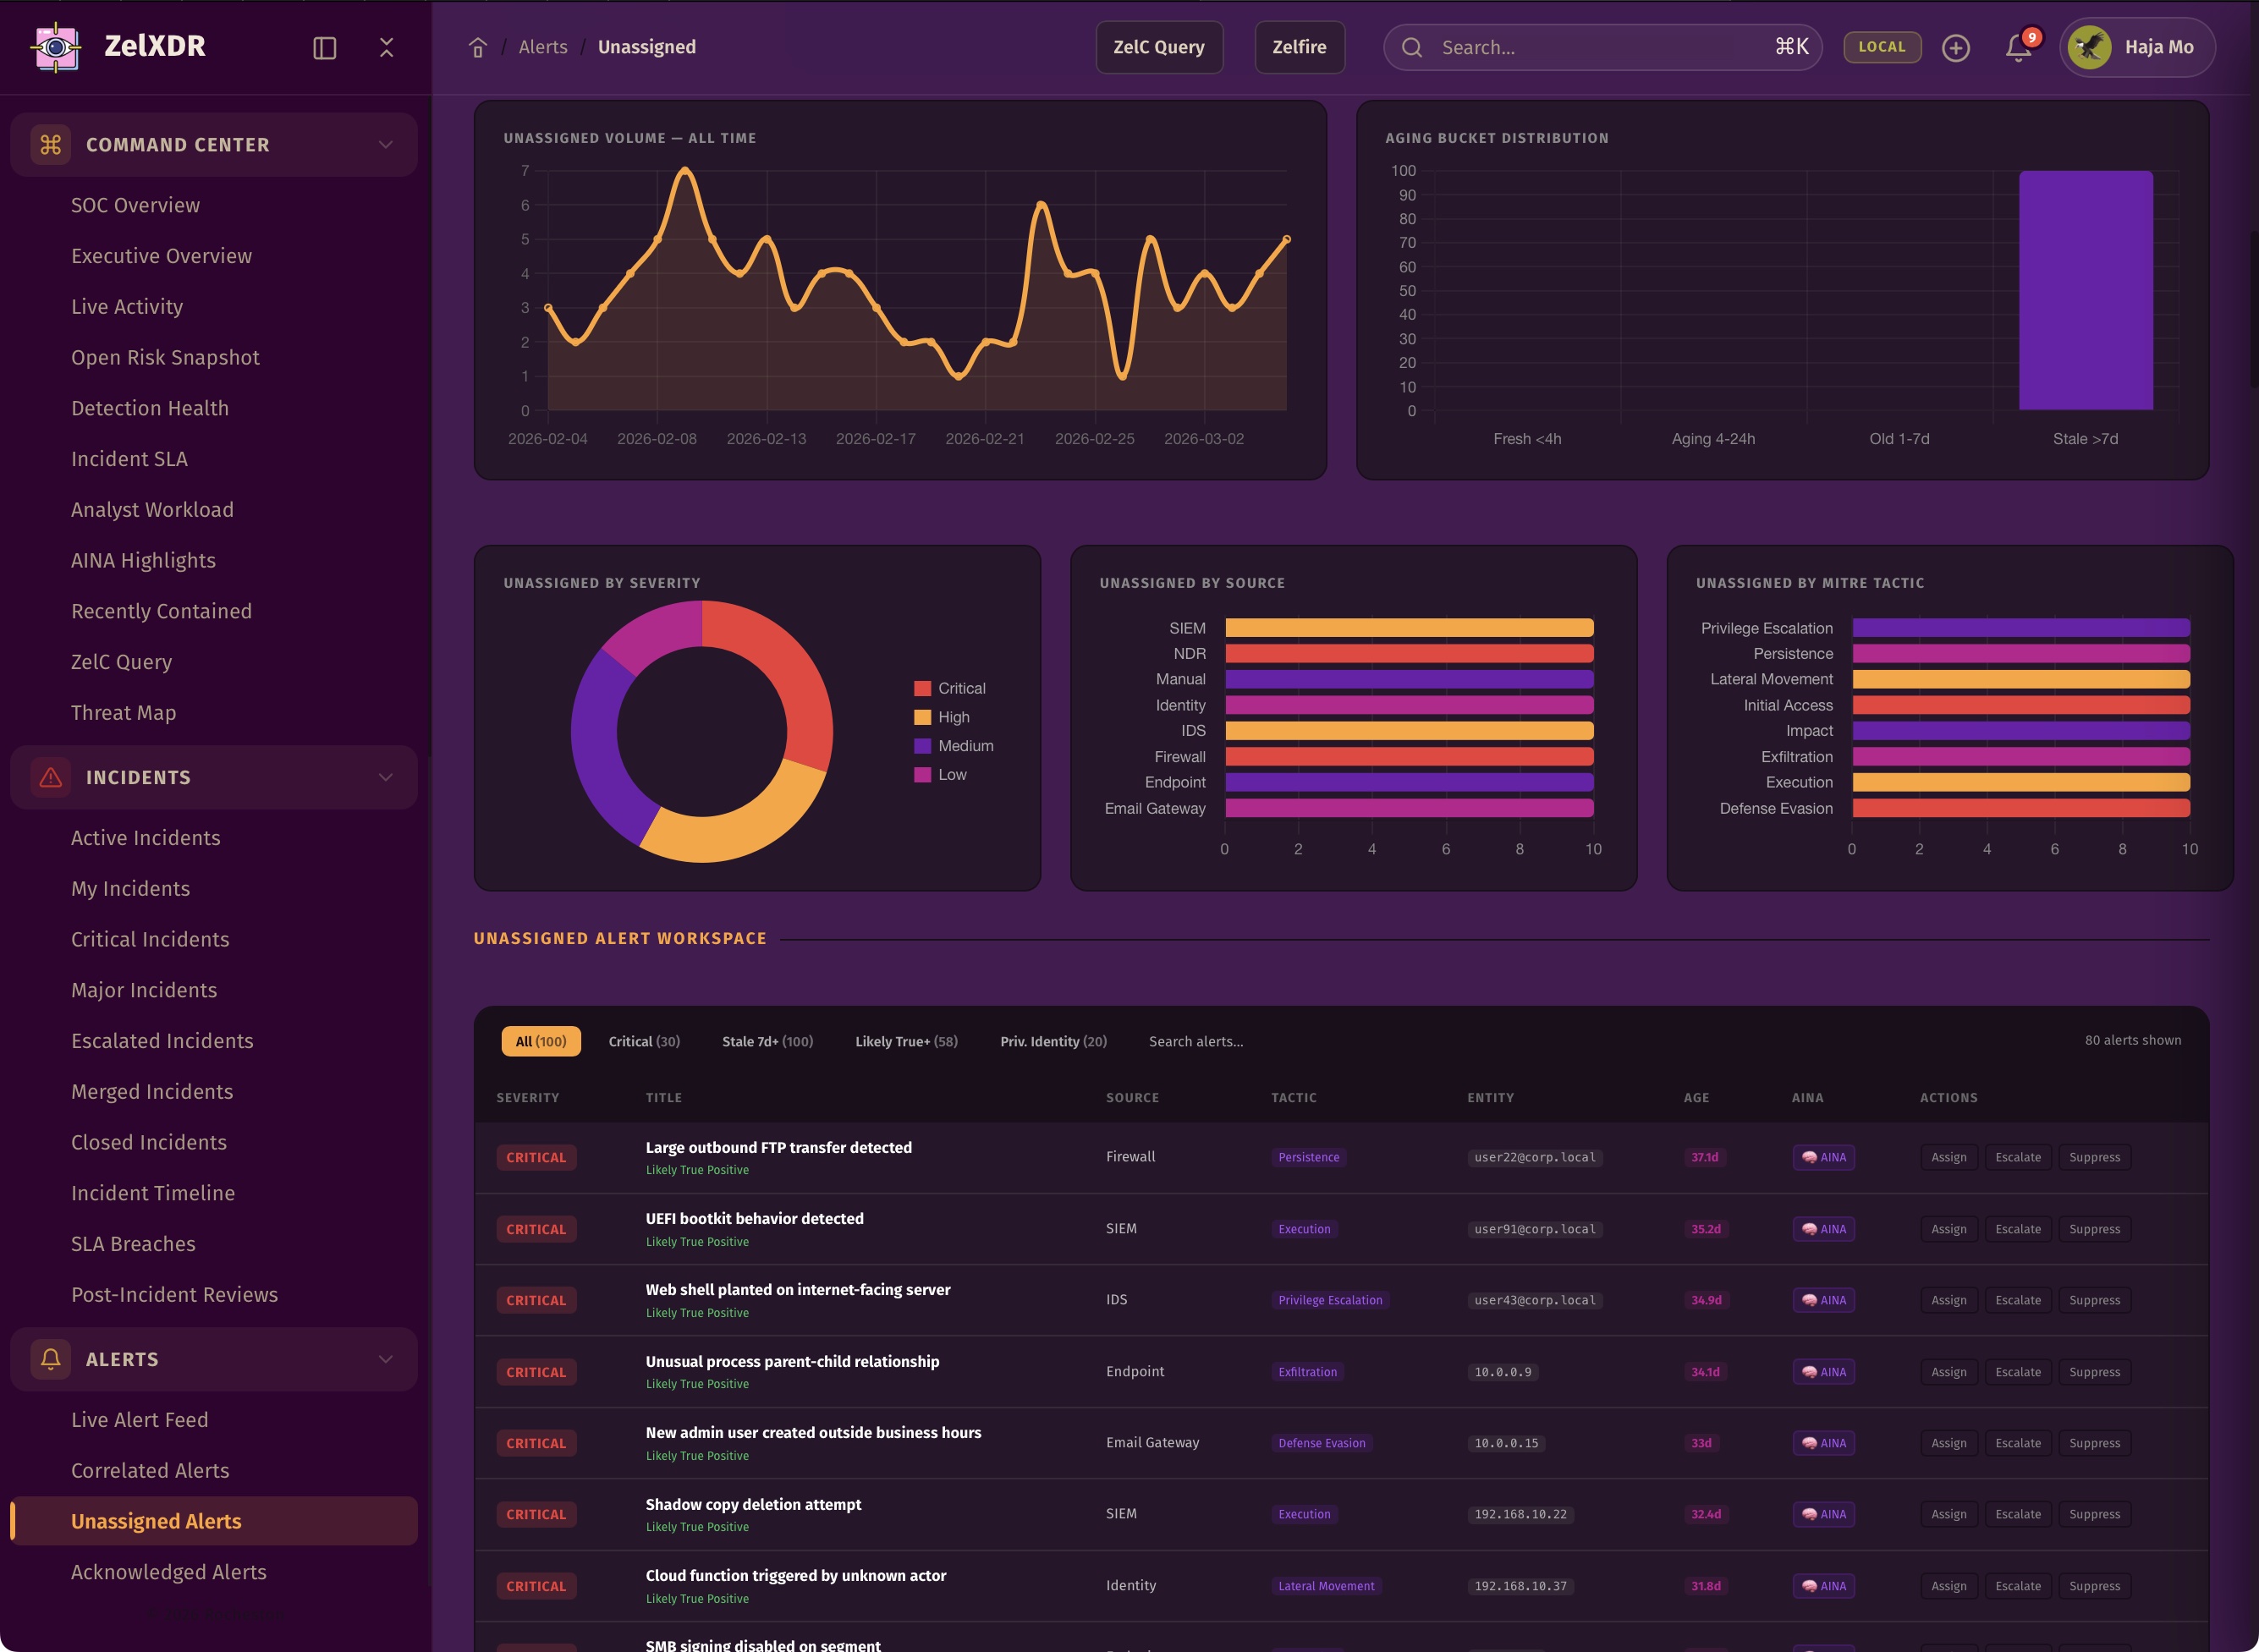
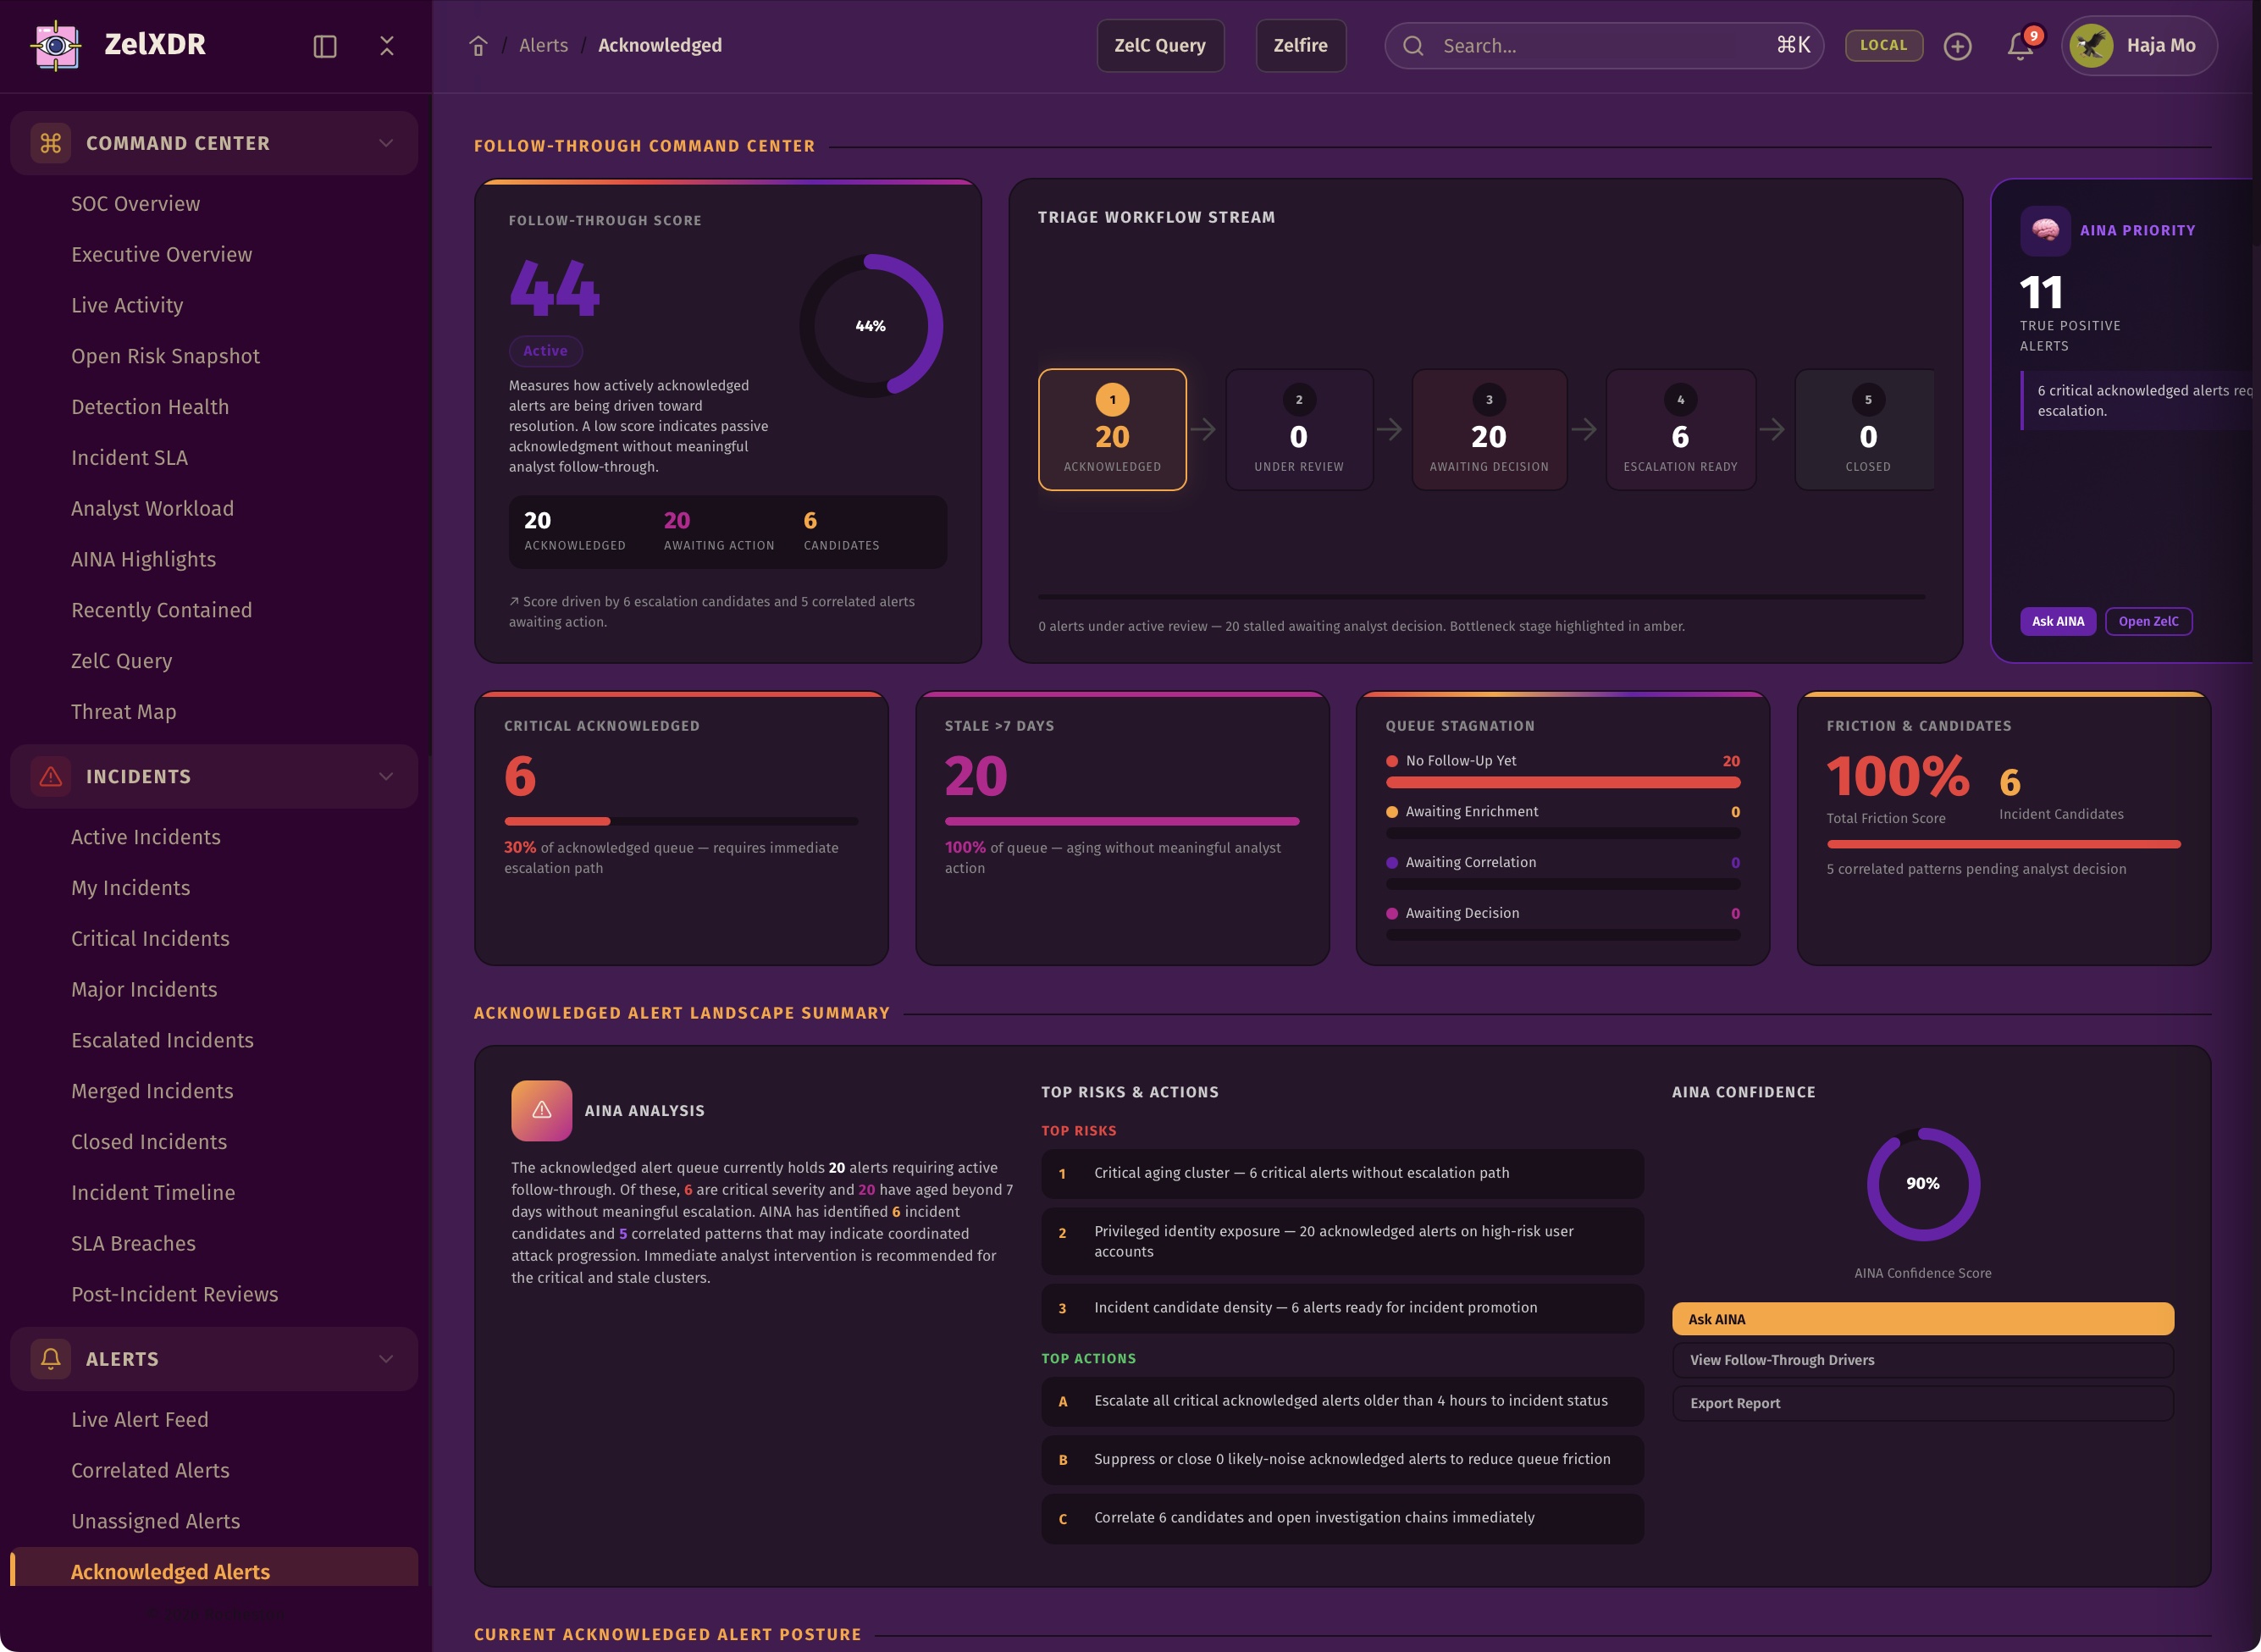
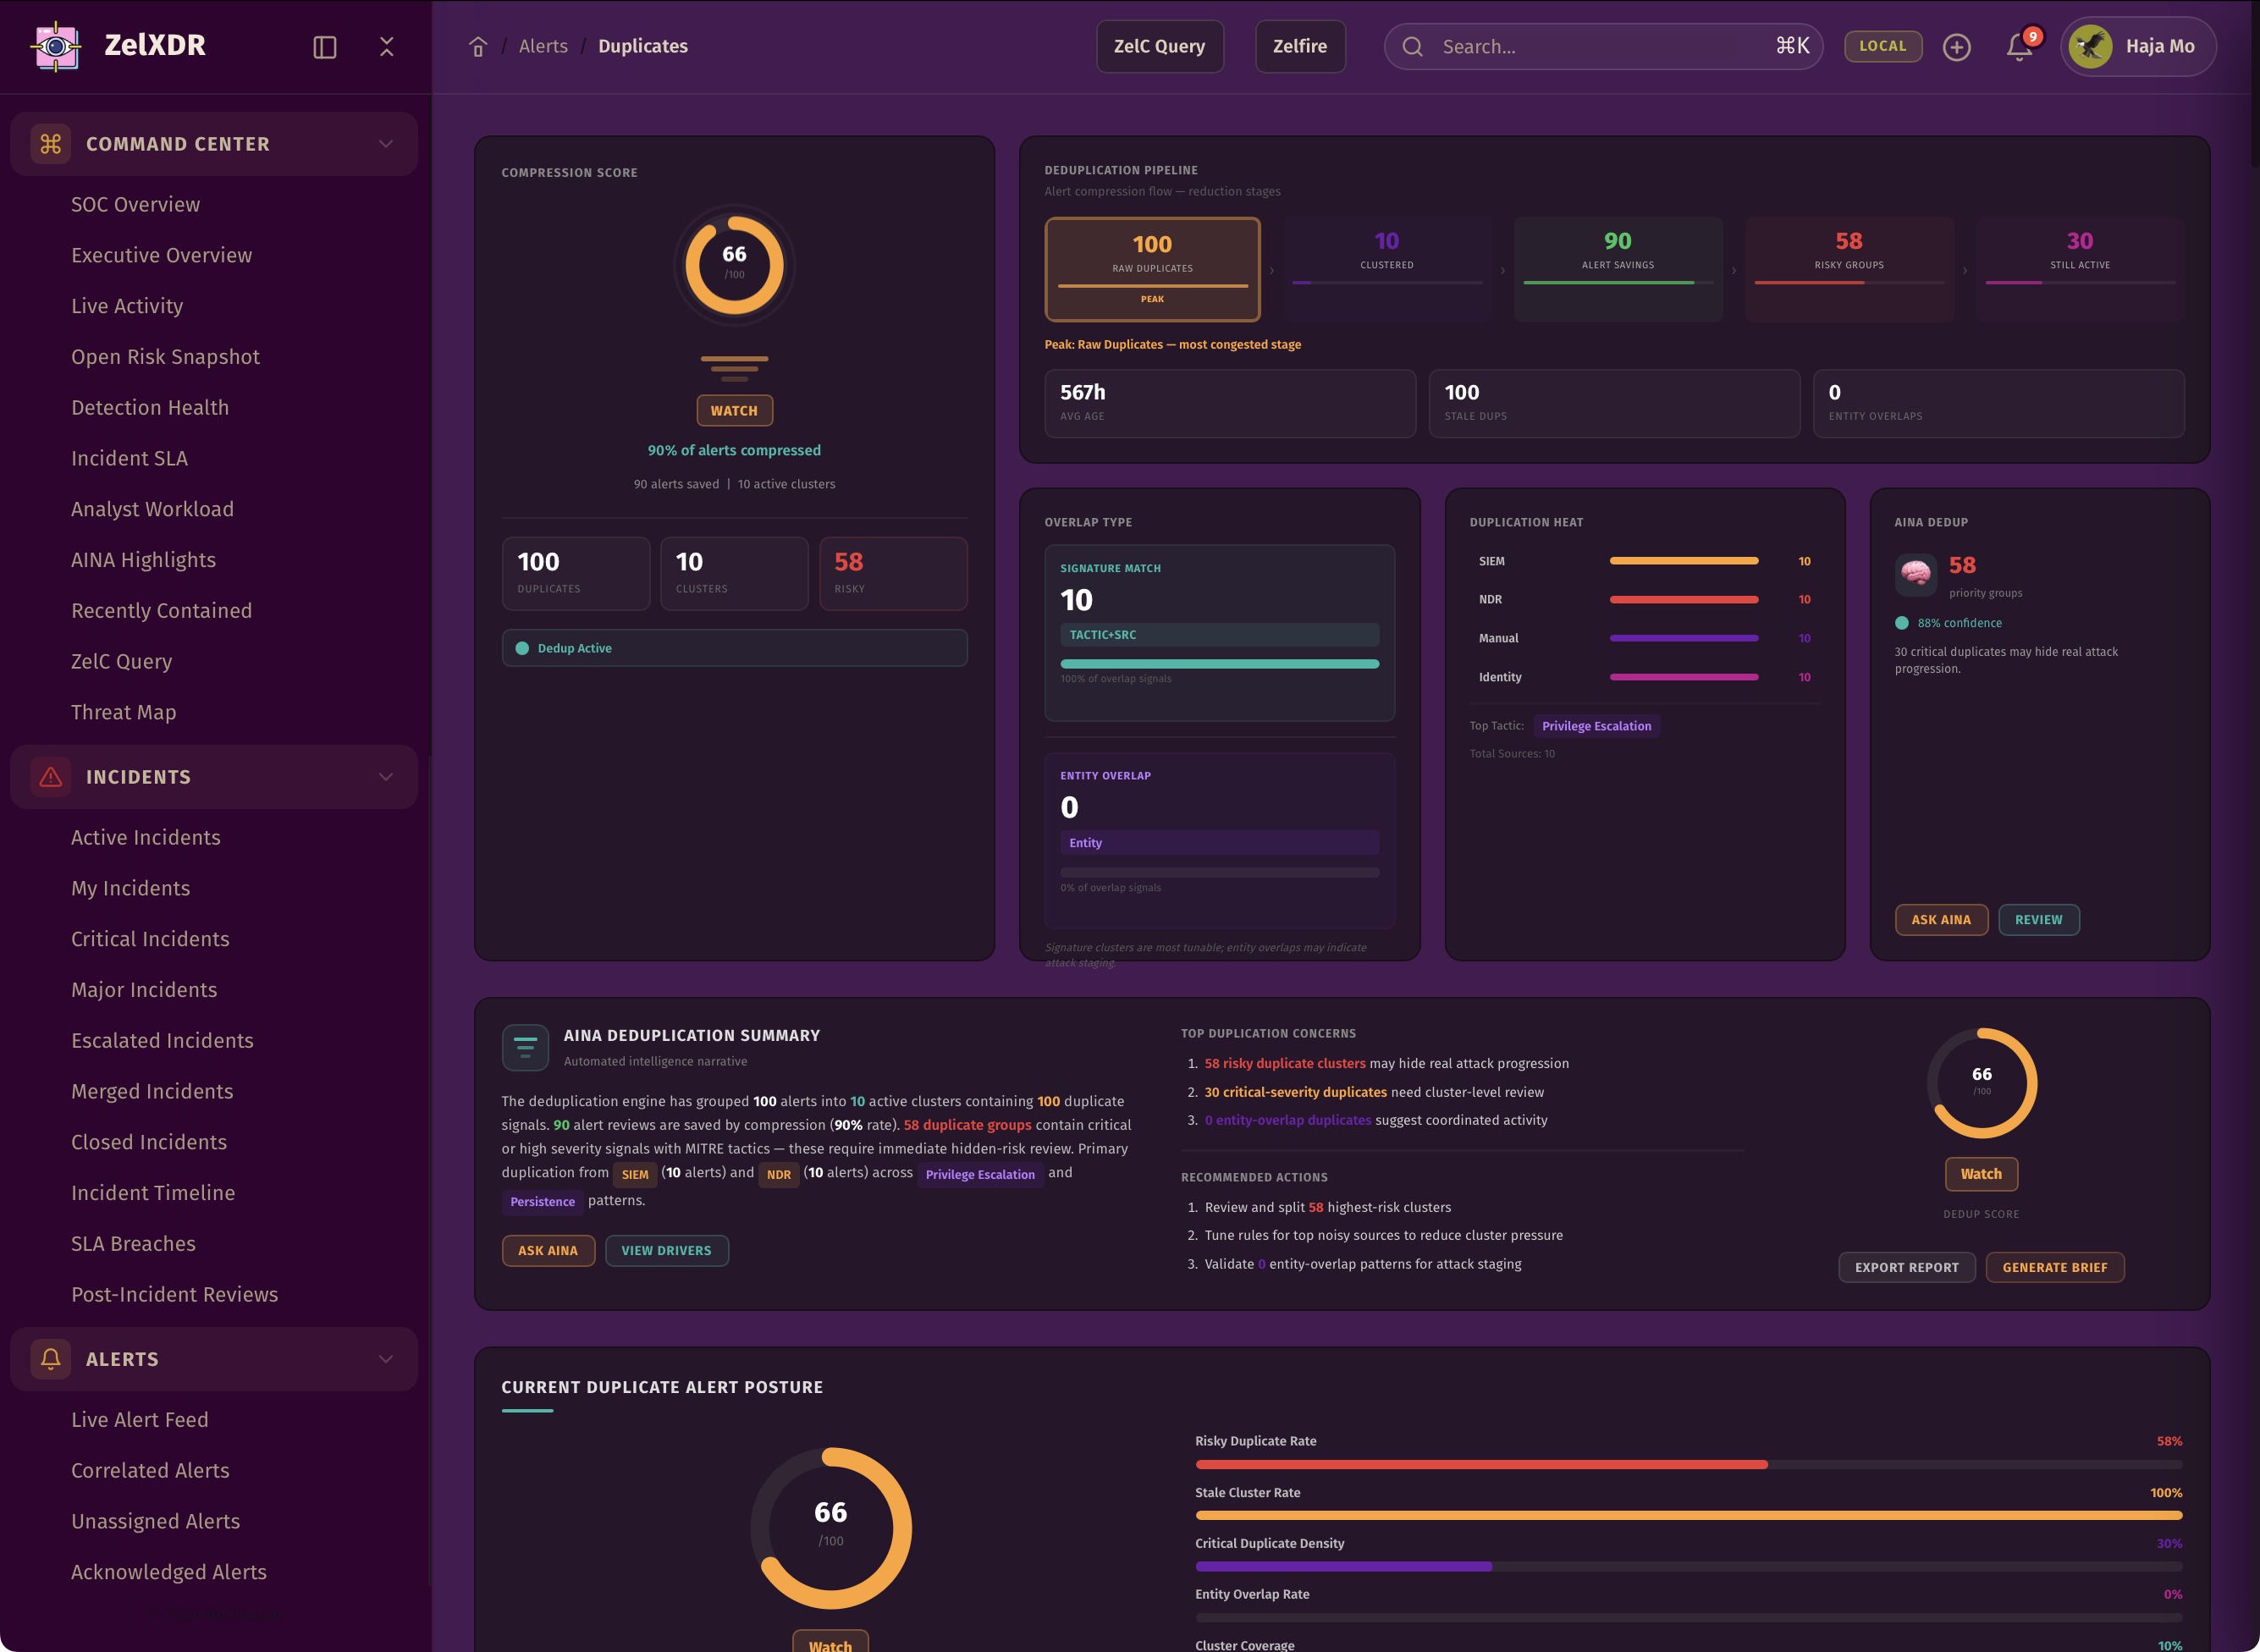
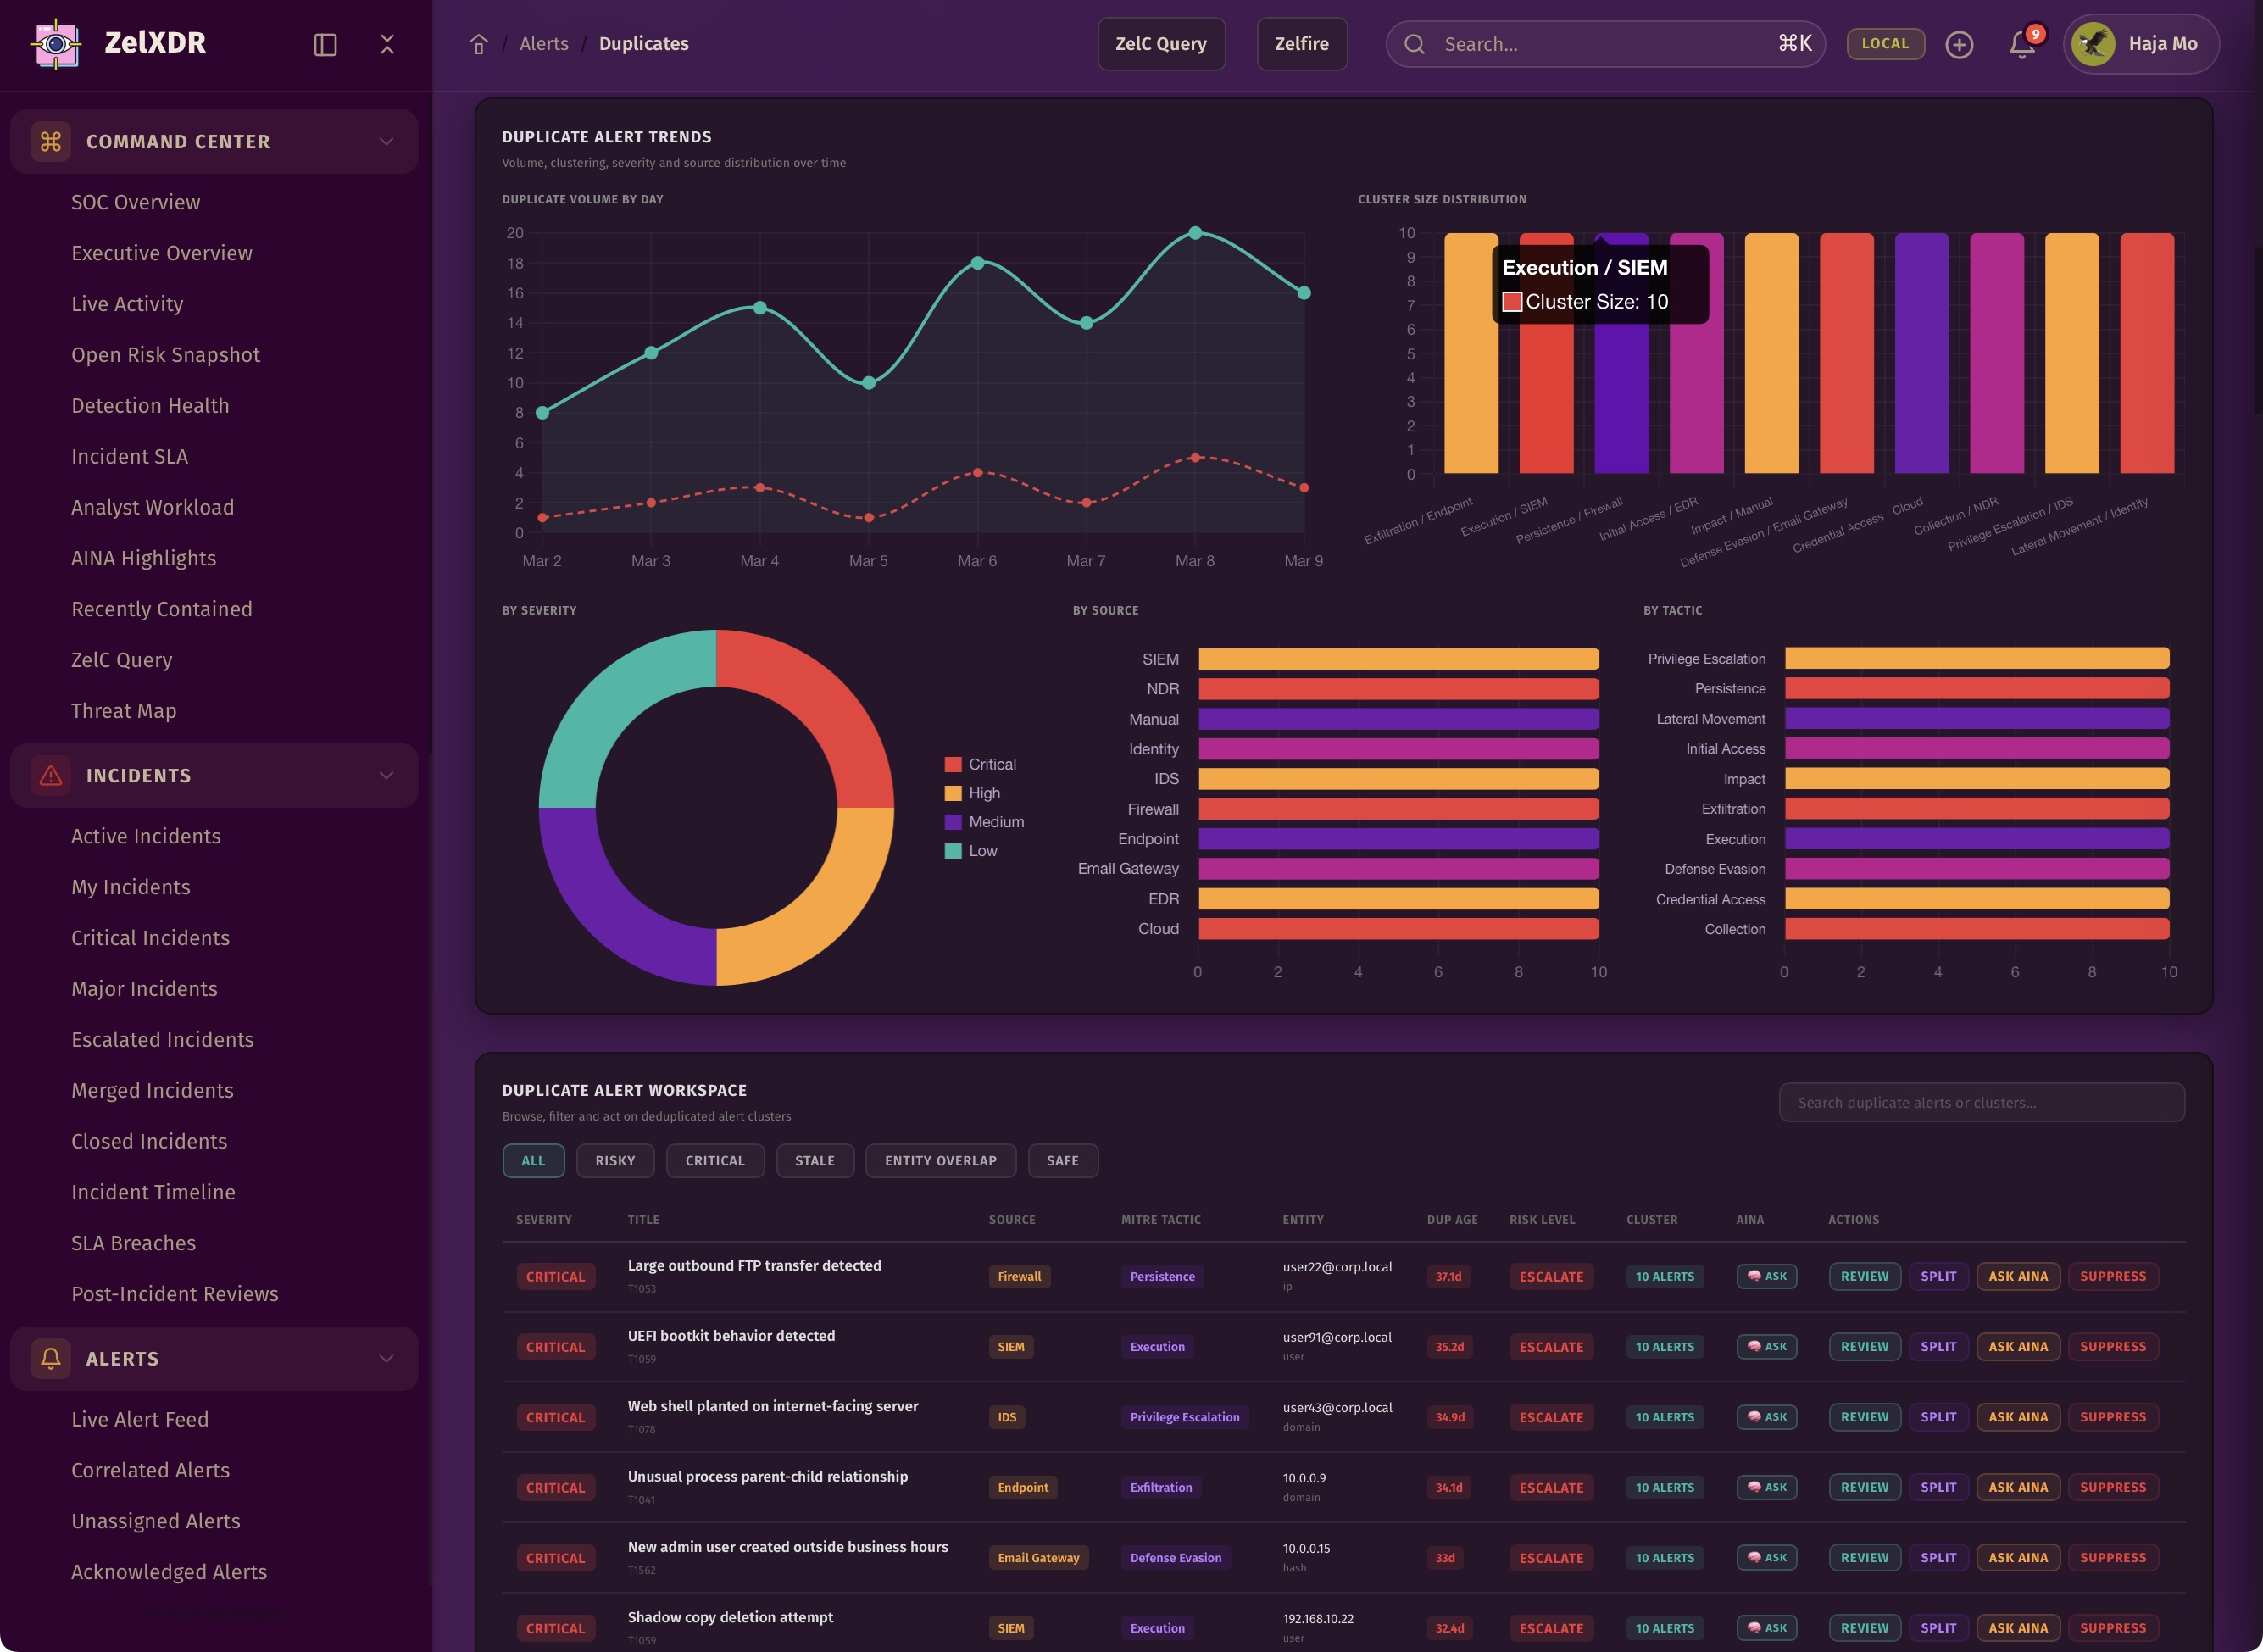
Not every alert deserves the same attention. ZelXDR helps teams surface the alerts that truly deserve escalation while quickly identifying false positives, duplicates, and low-value noise.
The right alert at the right time changes everything.
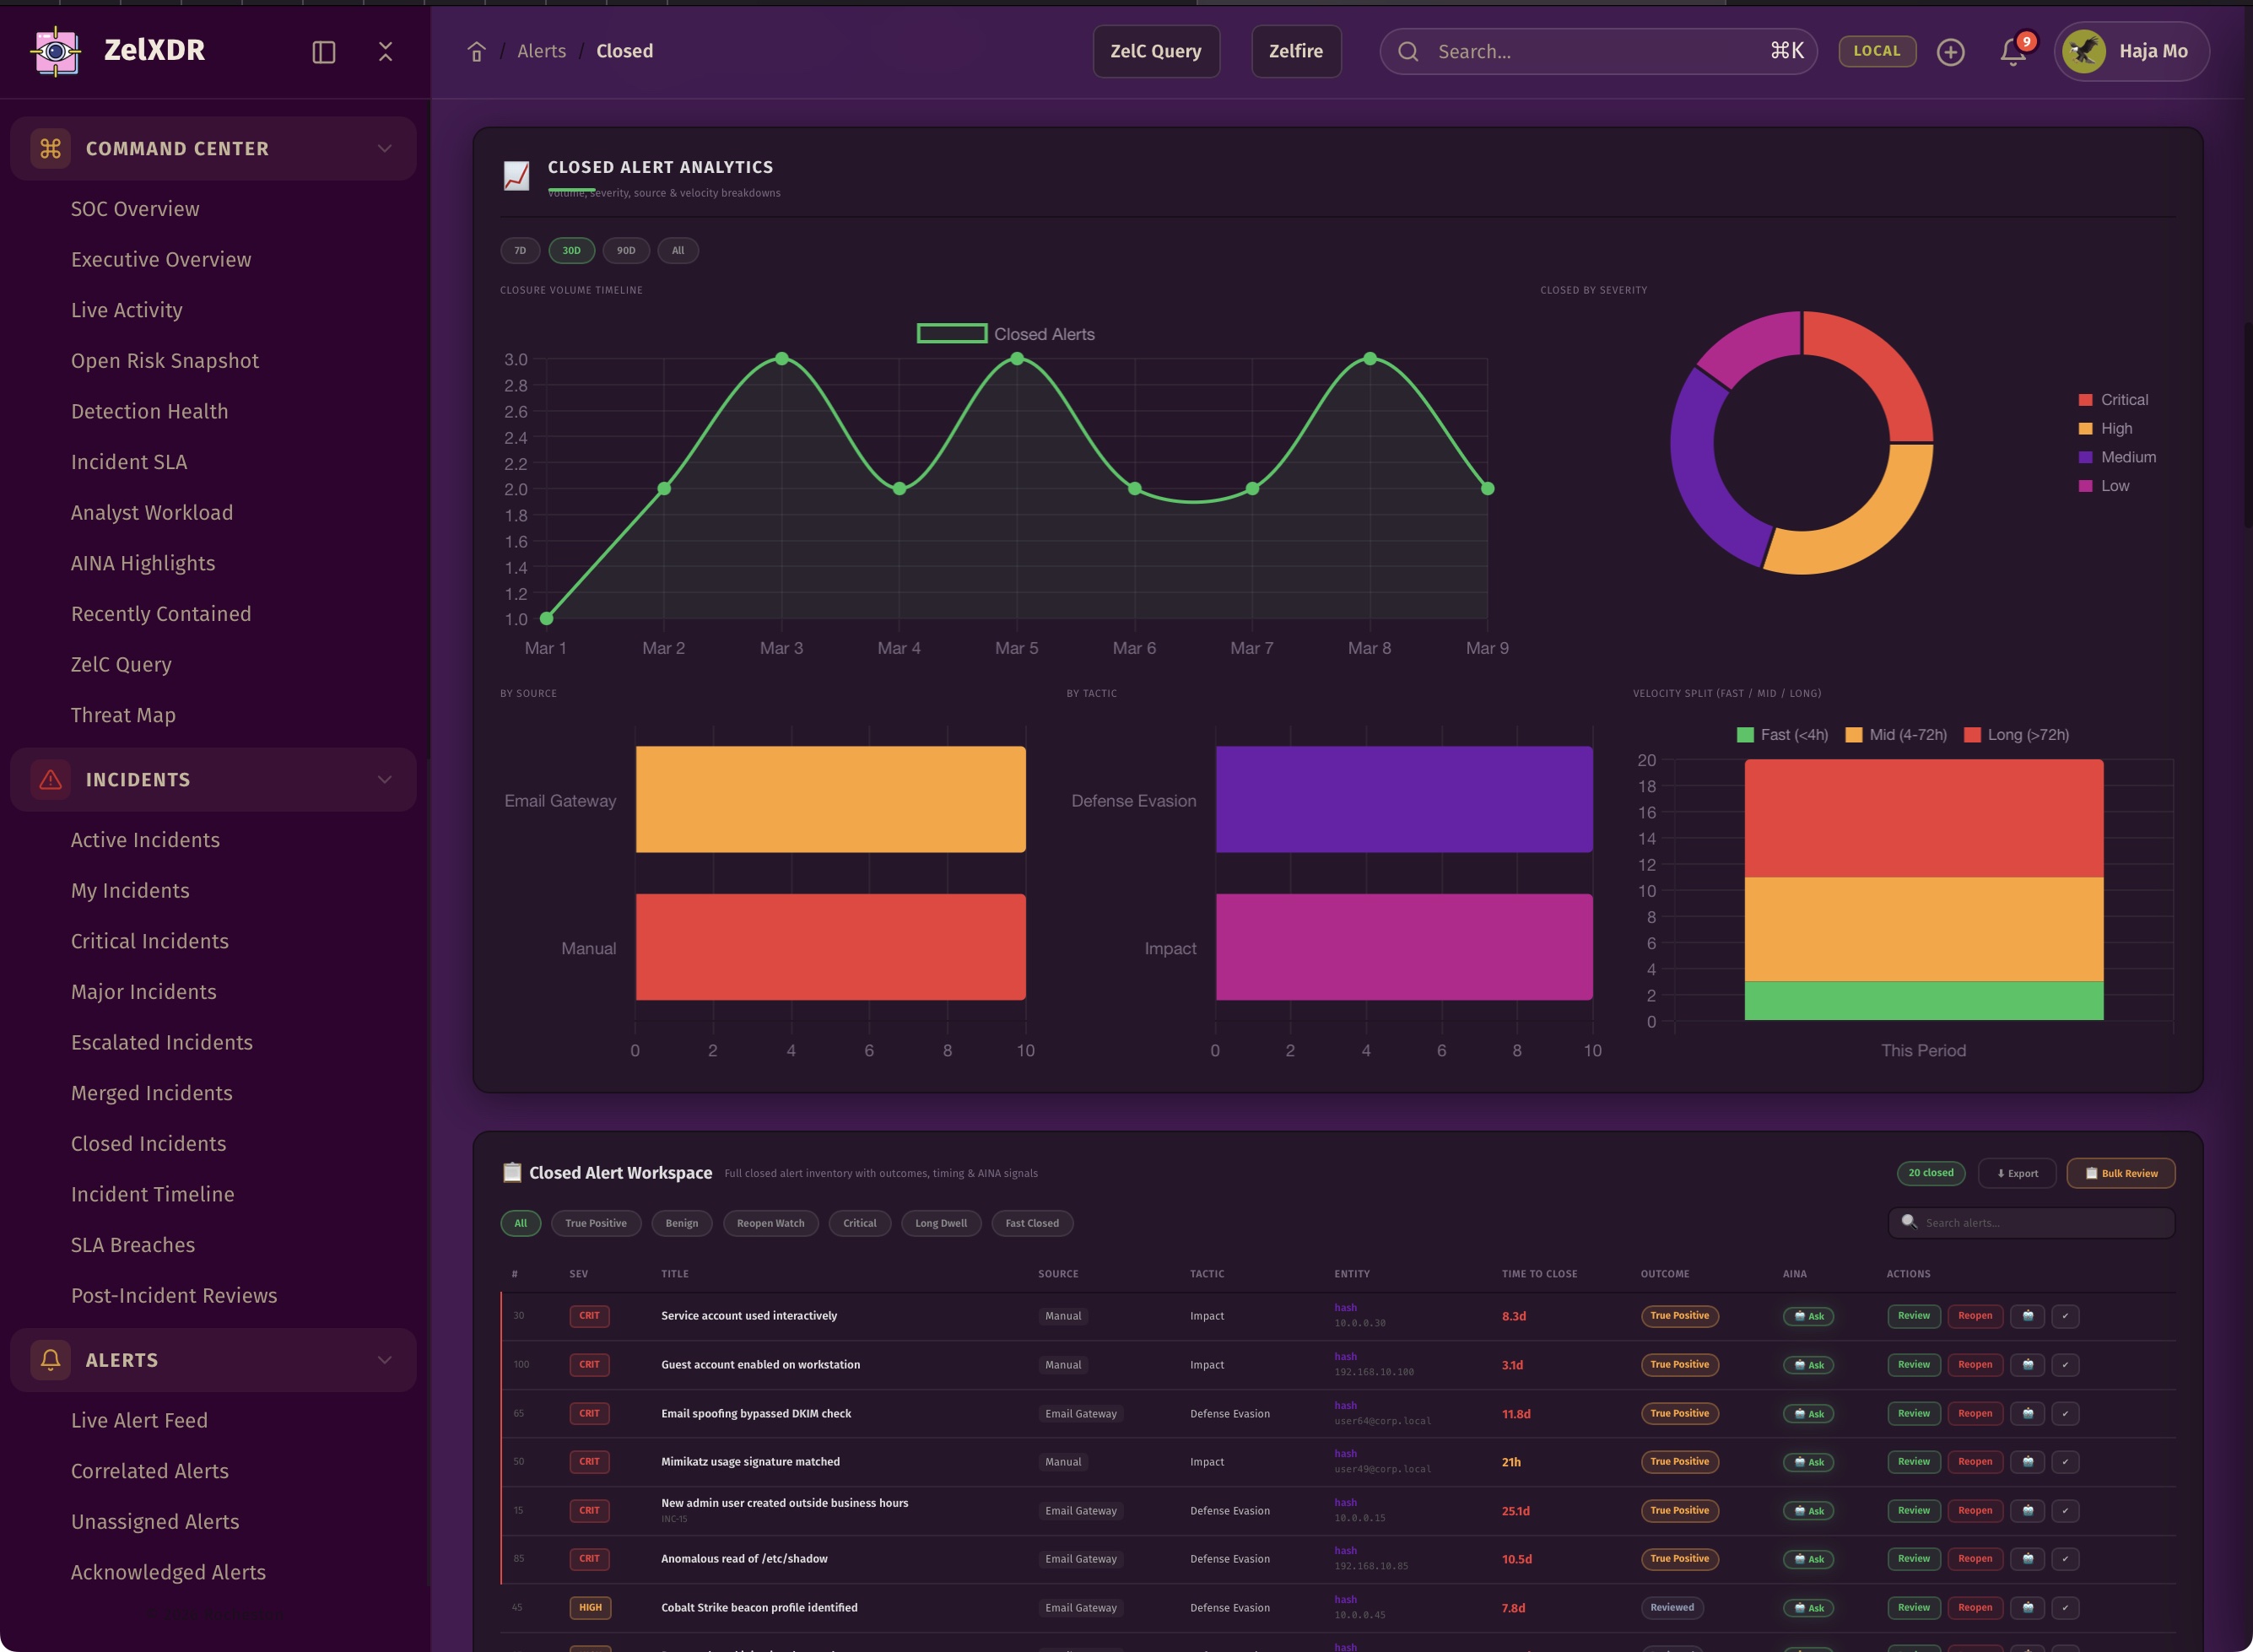
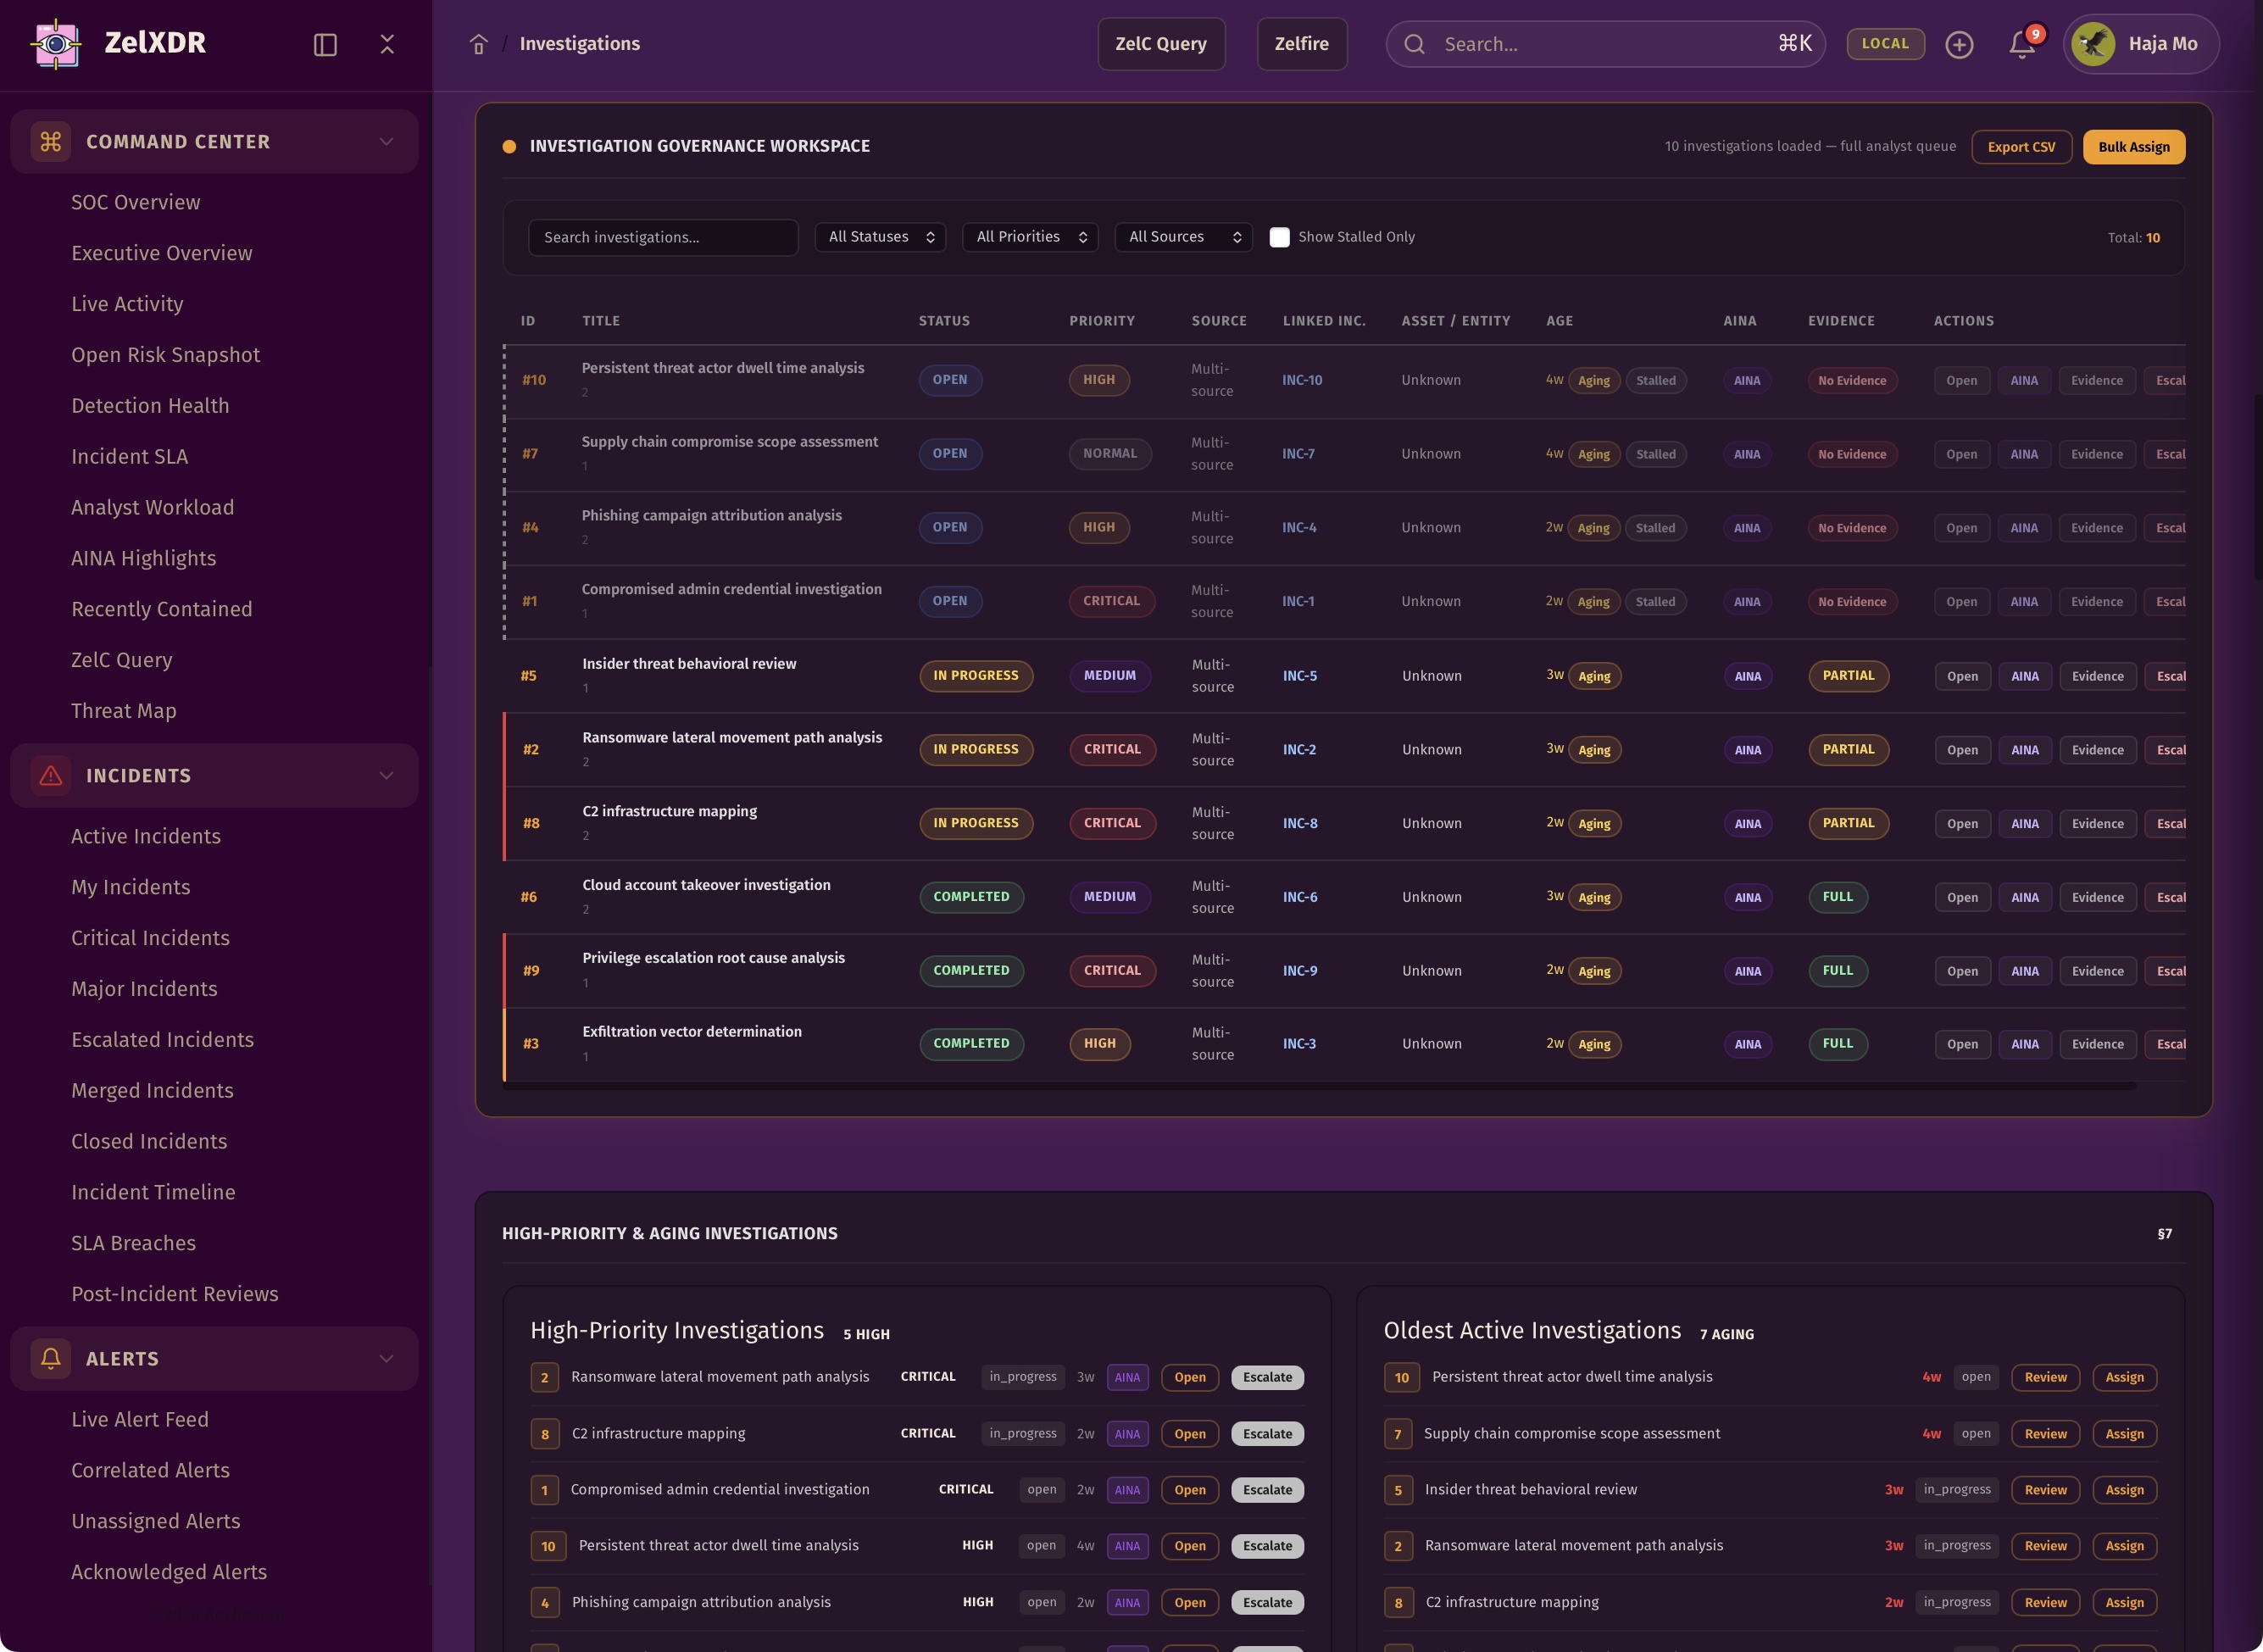
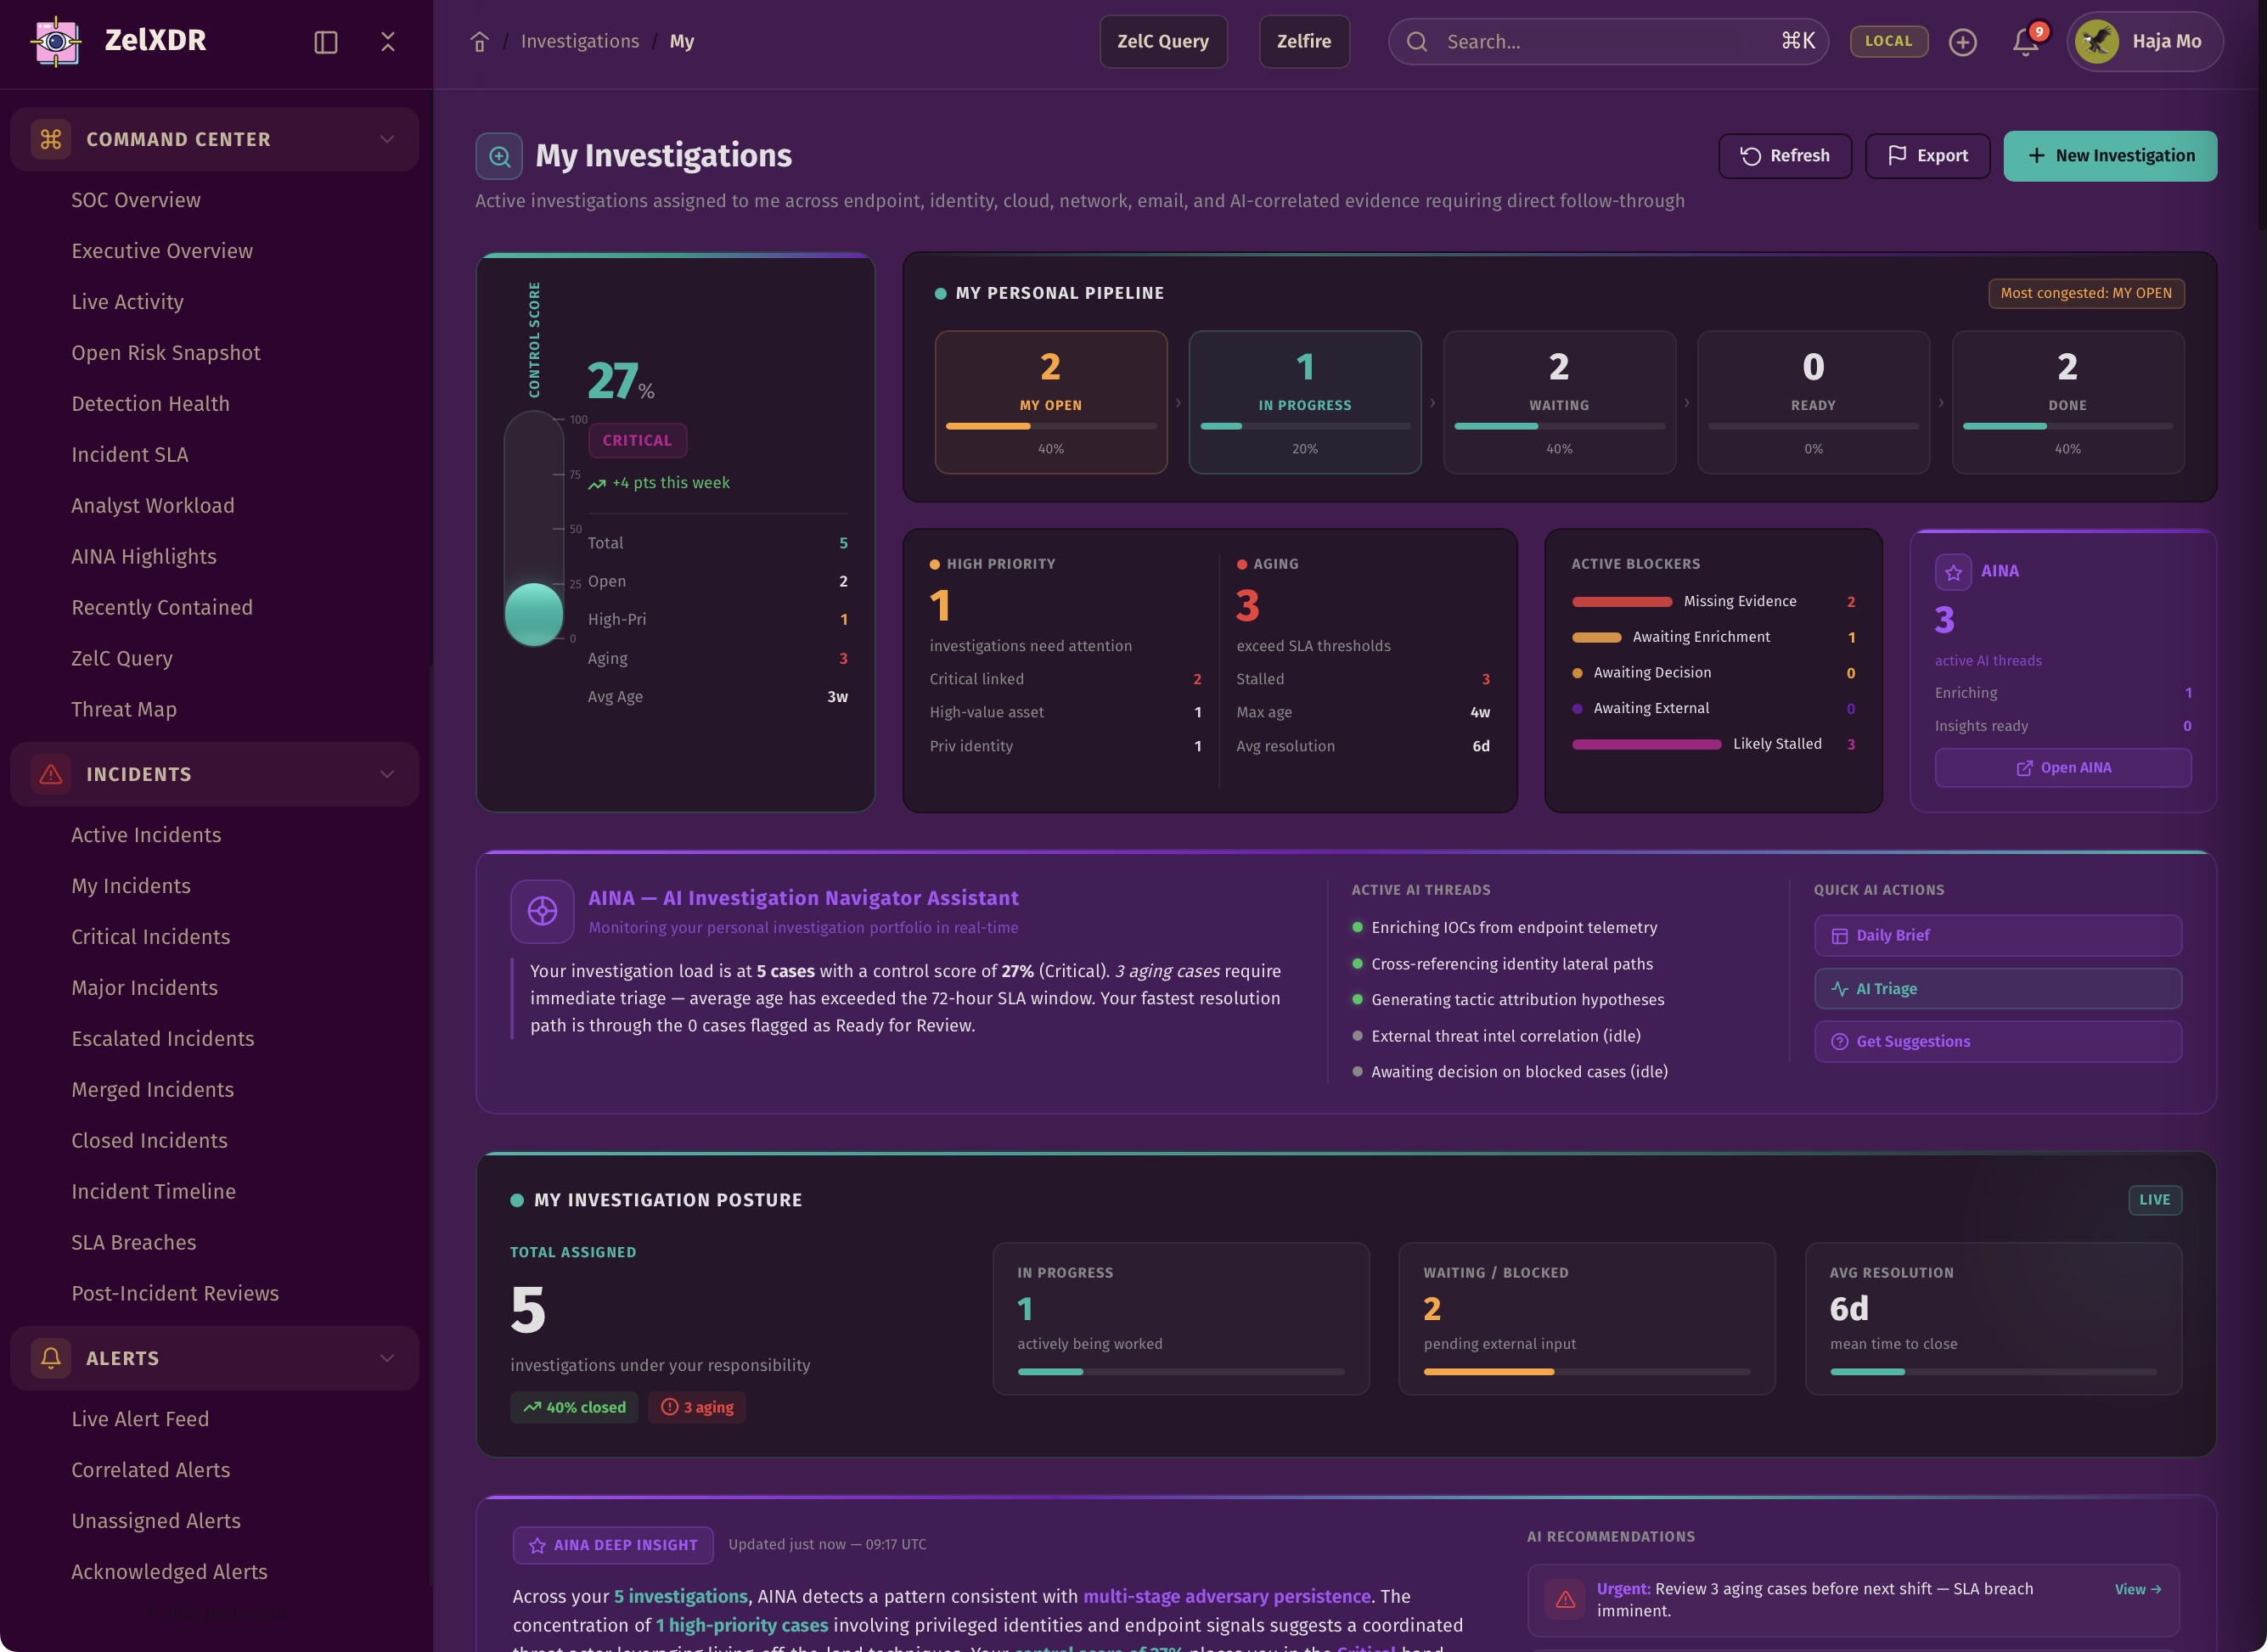
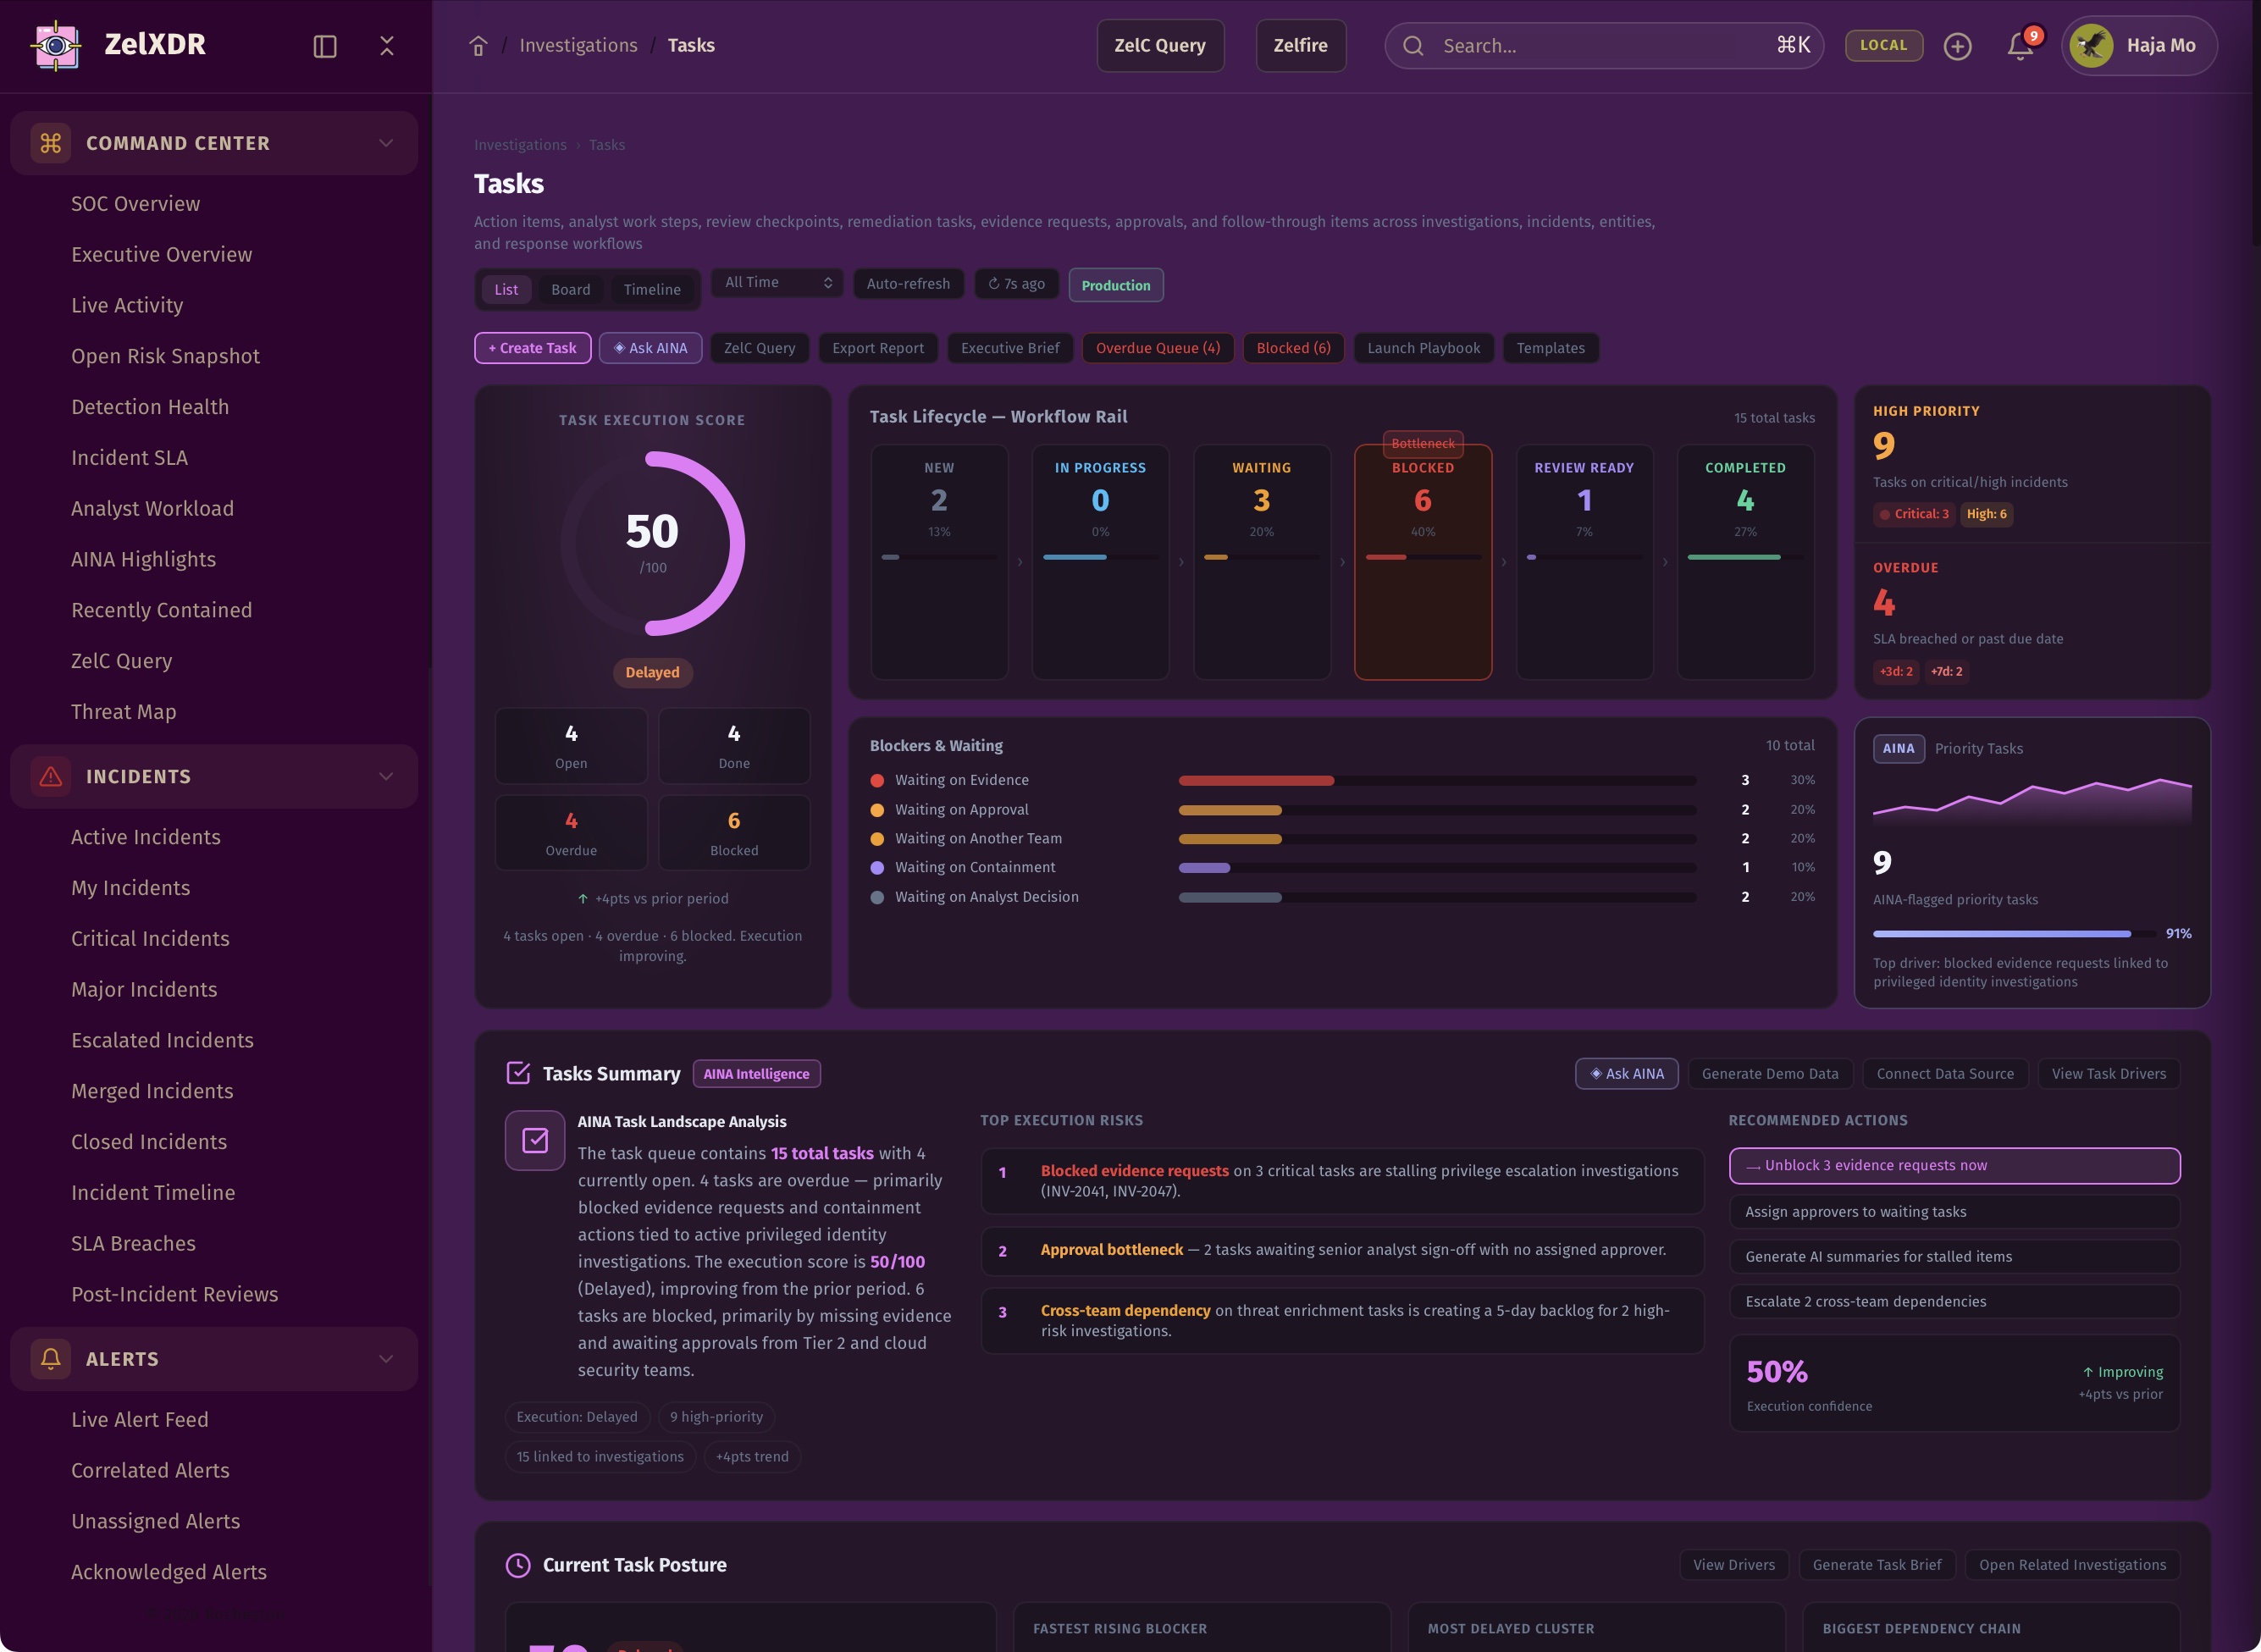
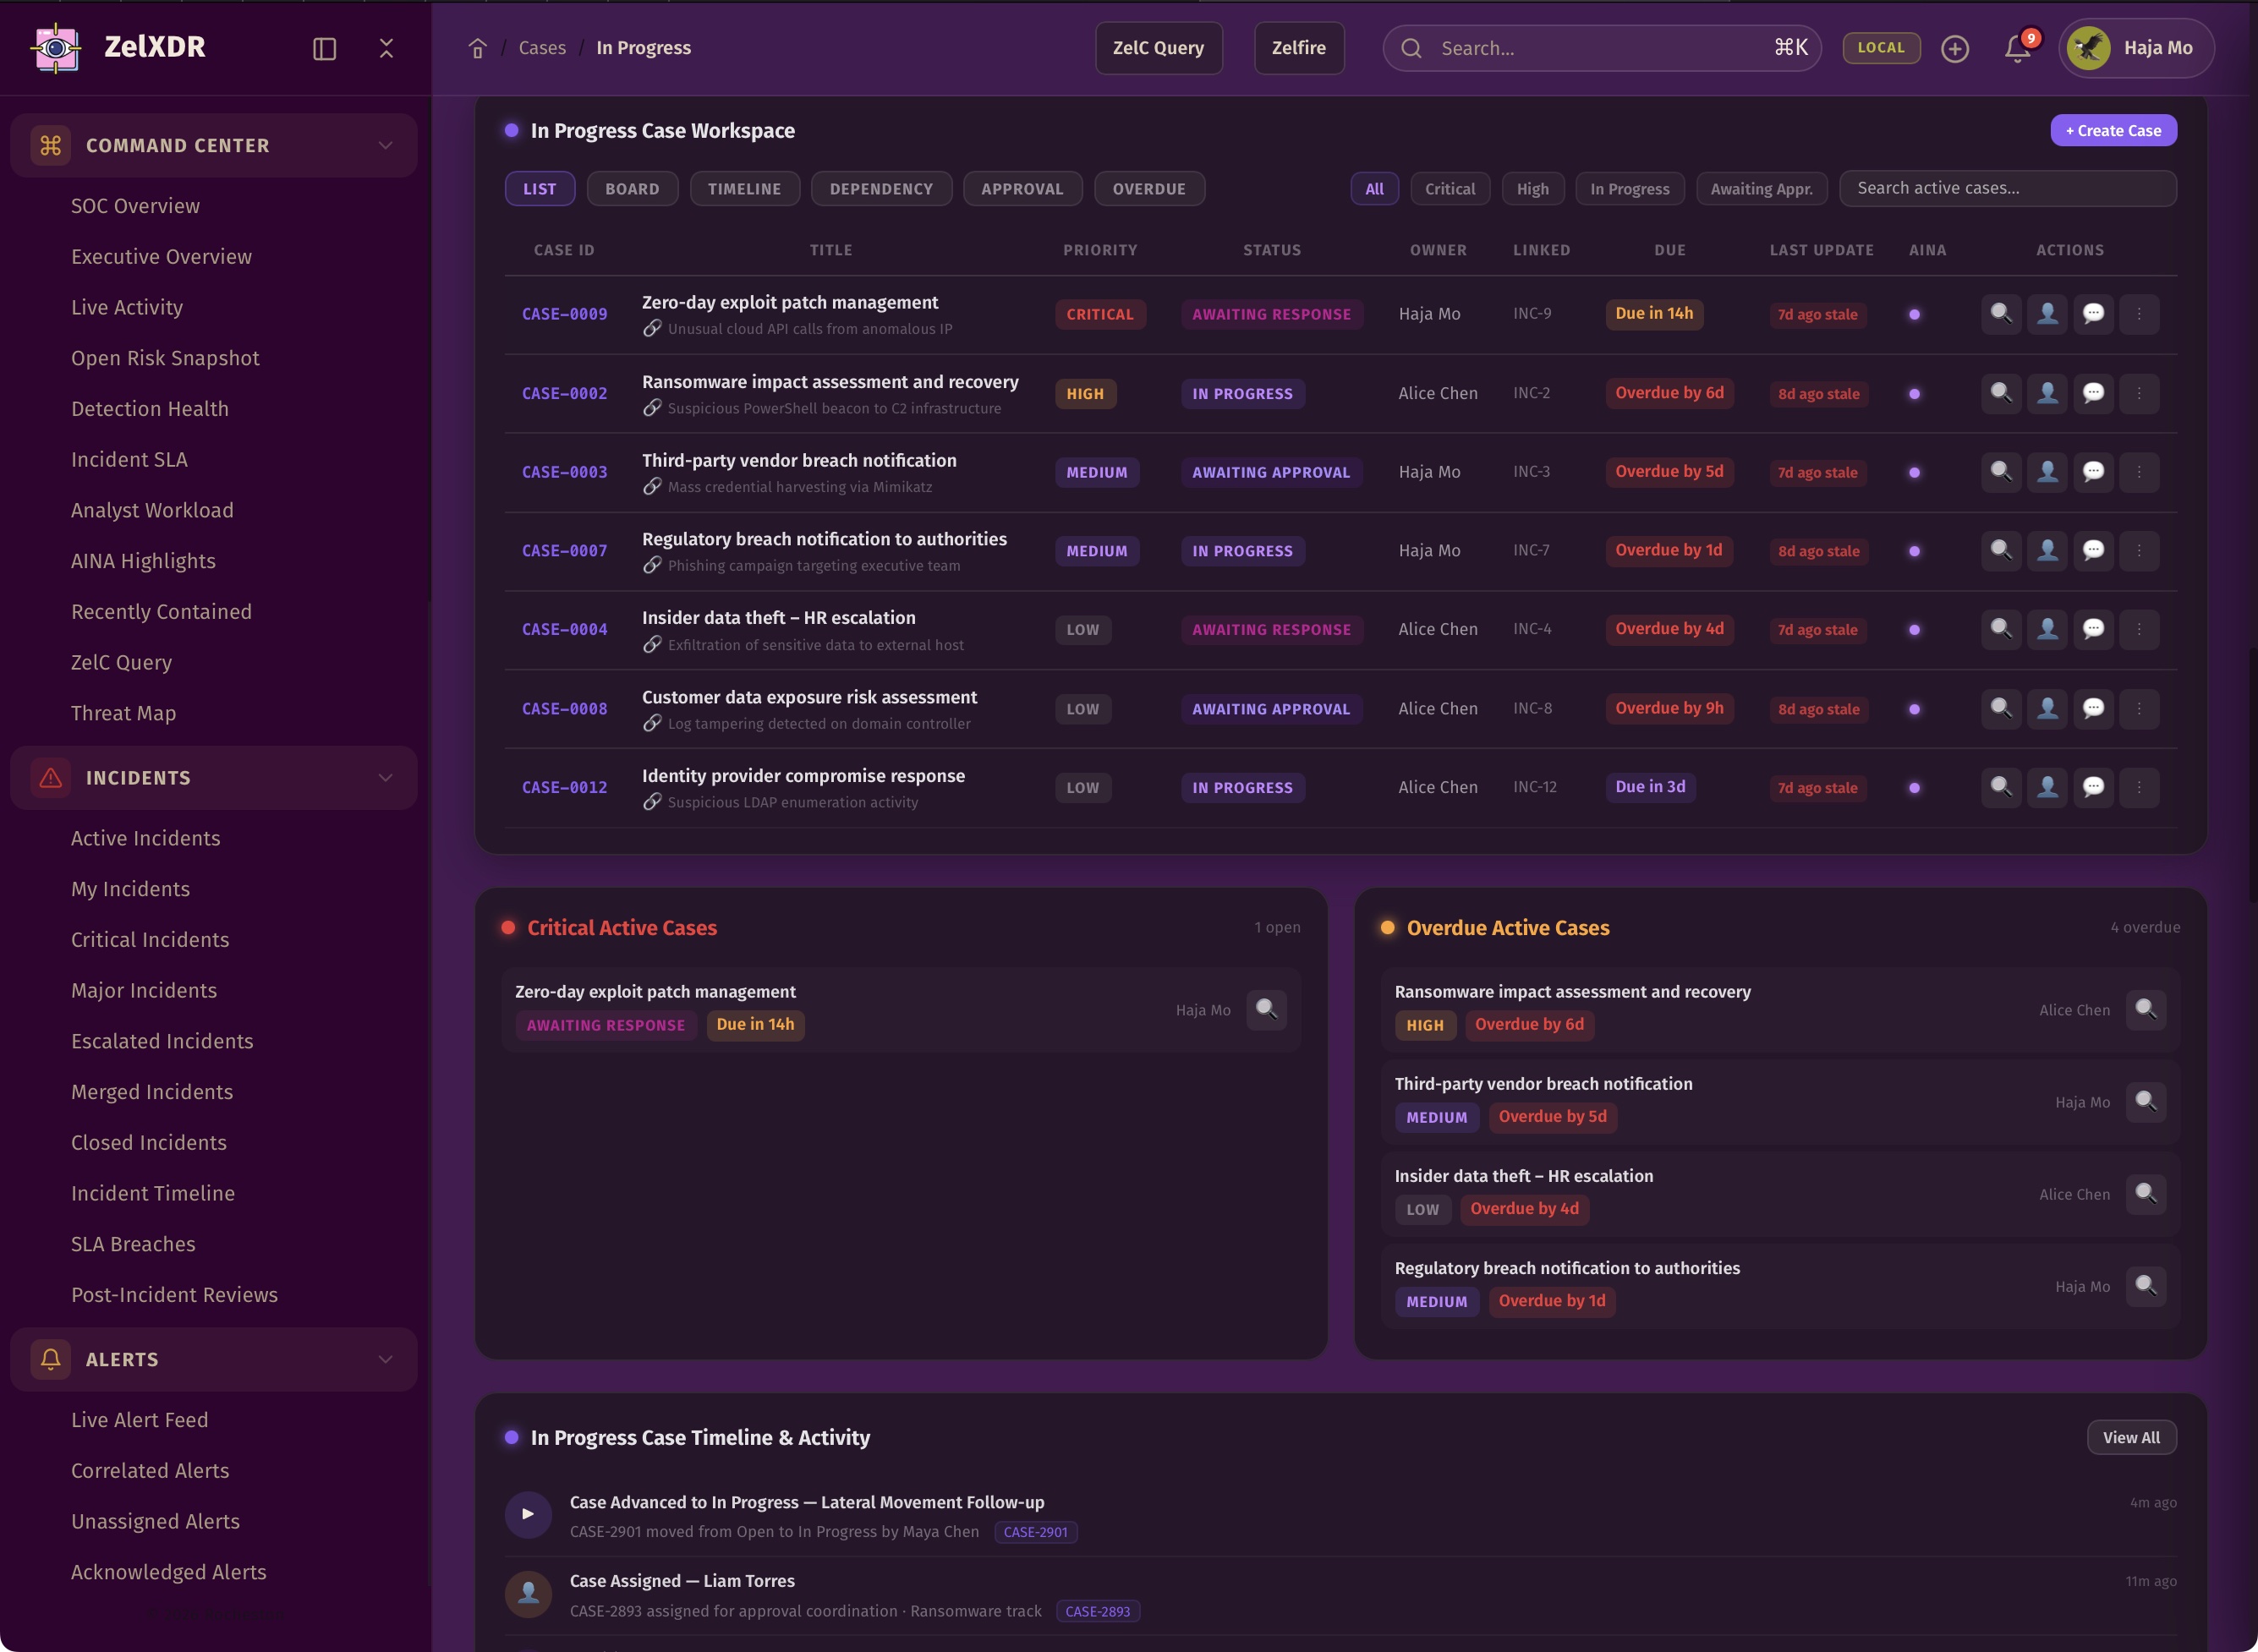
ZelXDR helps teams move from alert to investigation to response with less friction. Analysts can review evidence, understand impact, coordinate actions, and drive containment from one unified workflow.
Speed without context is chaos. ZelXDR delivers both.
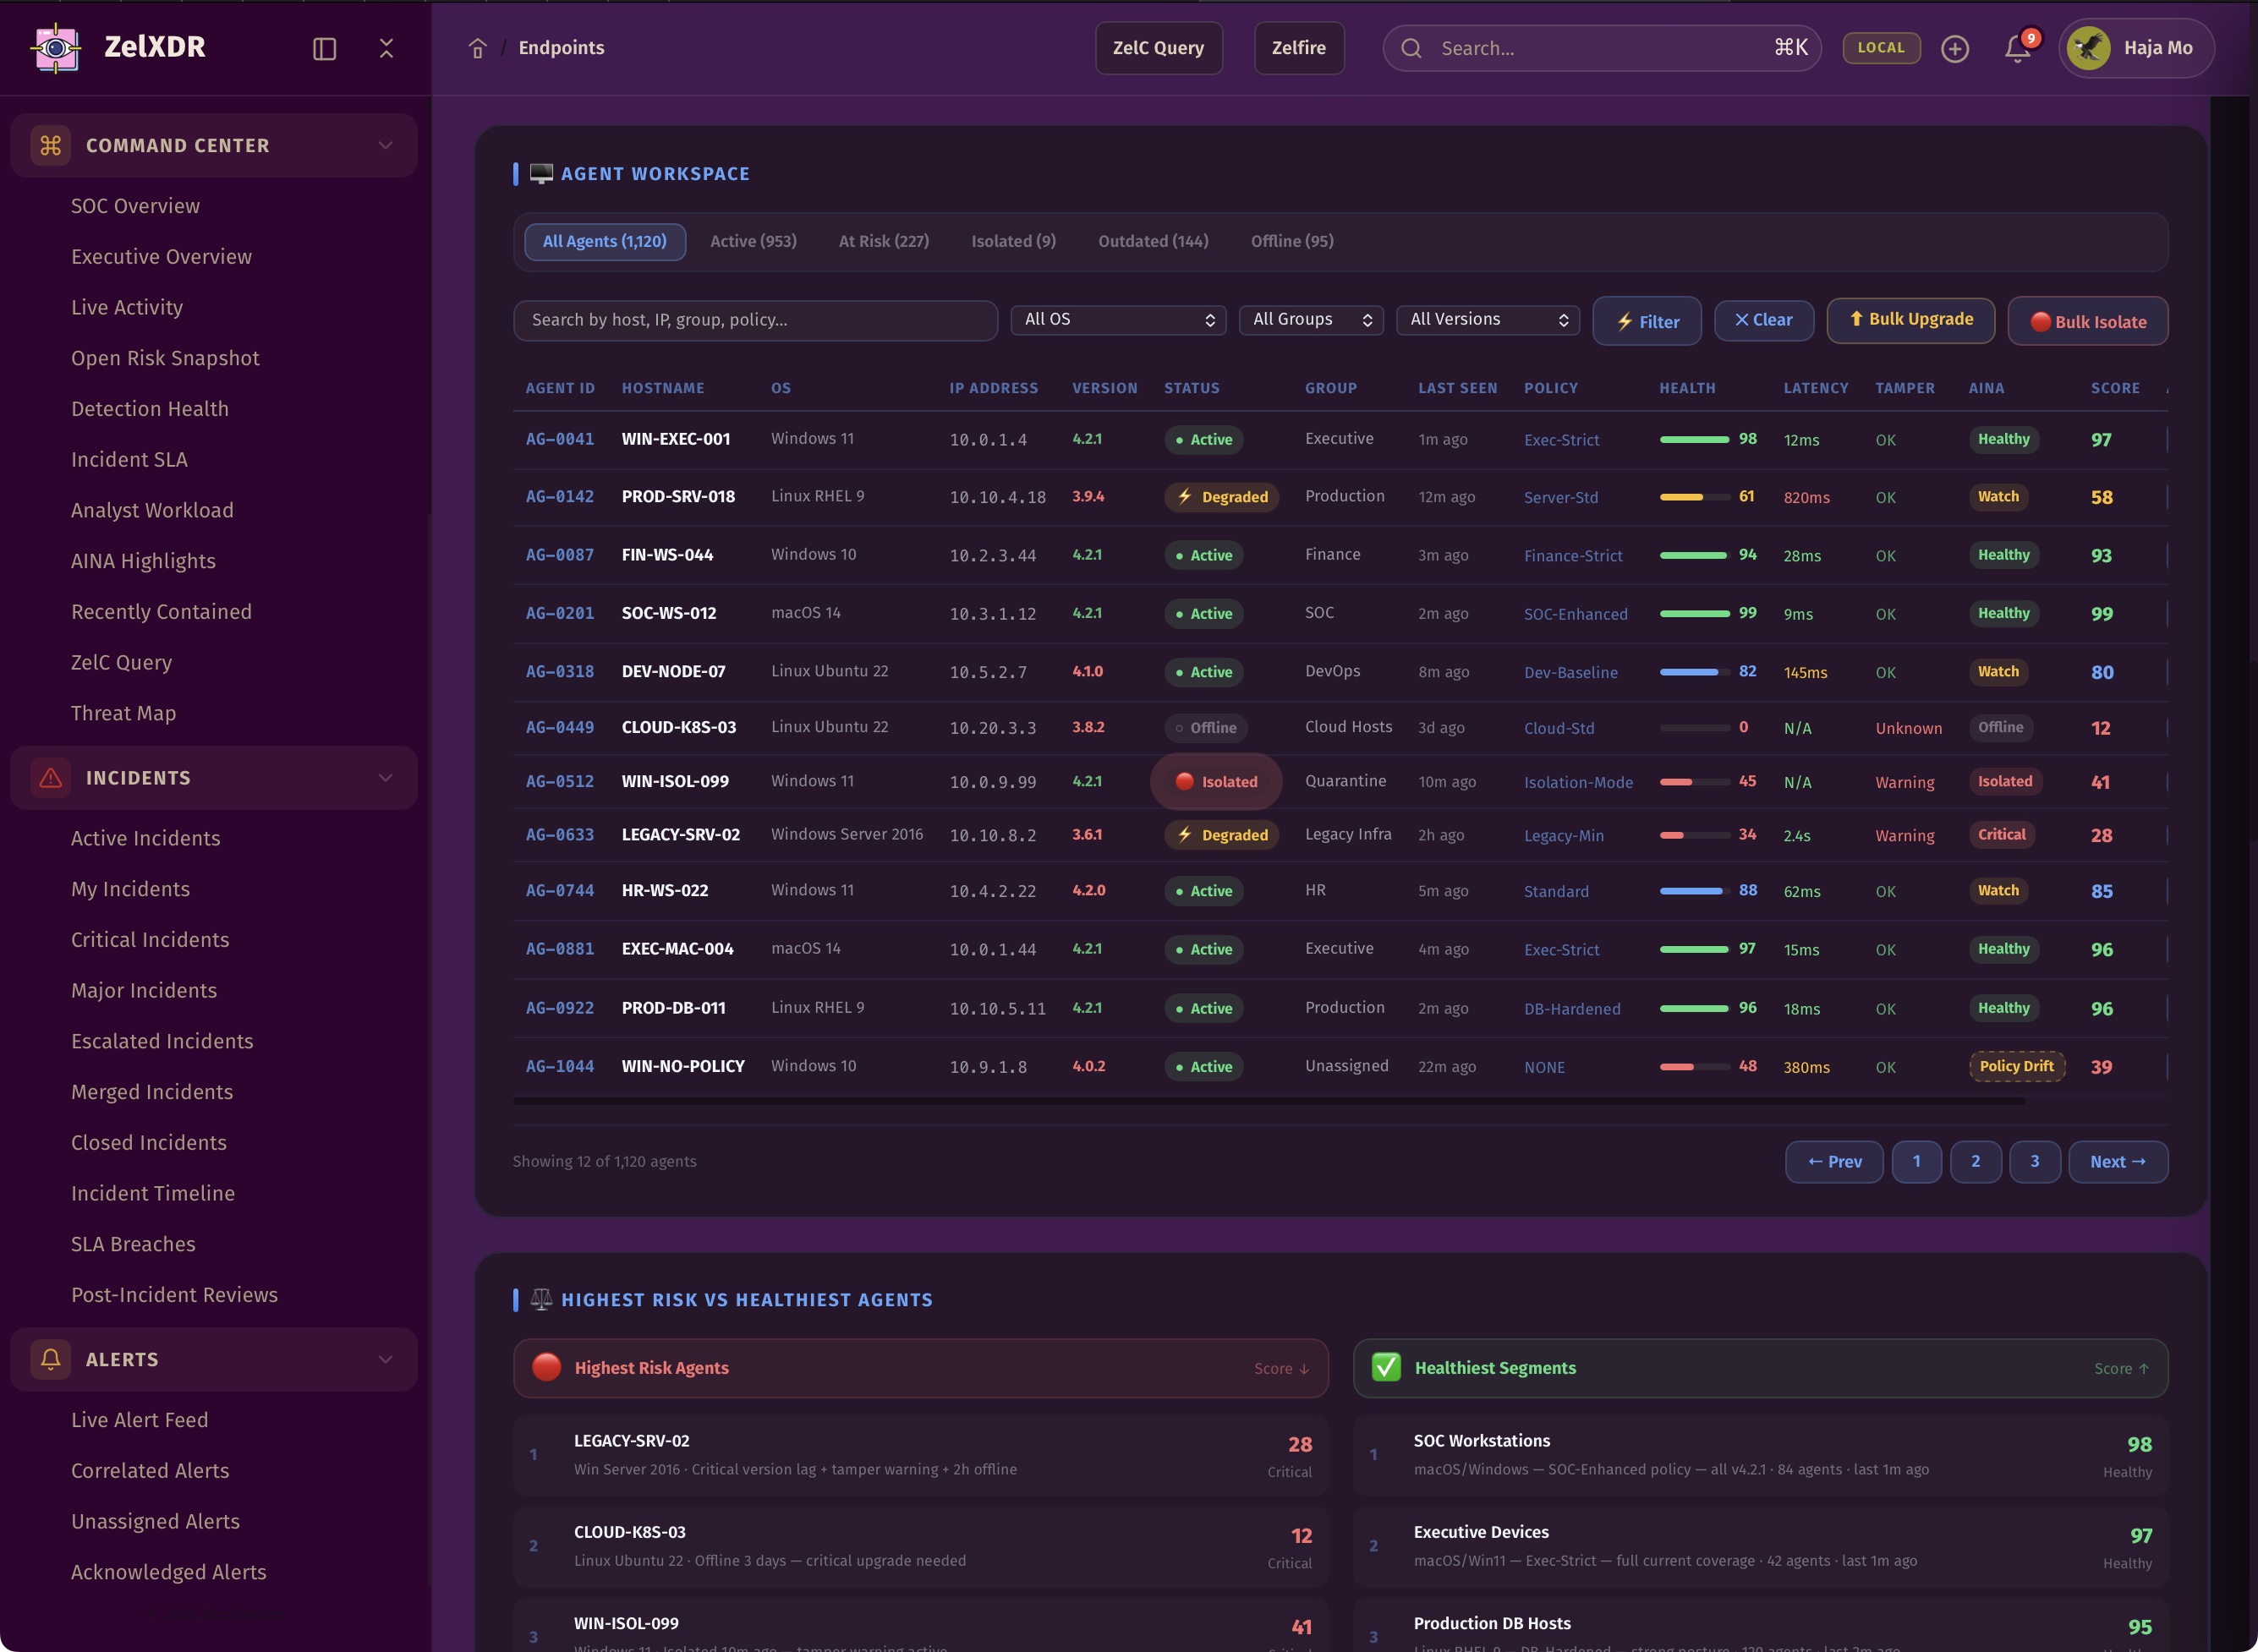
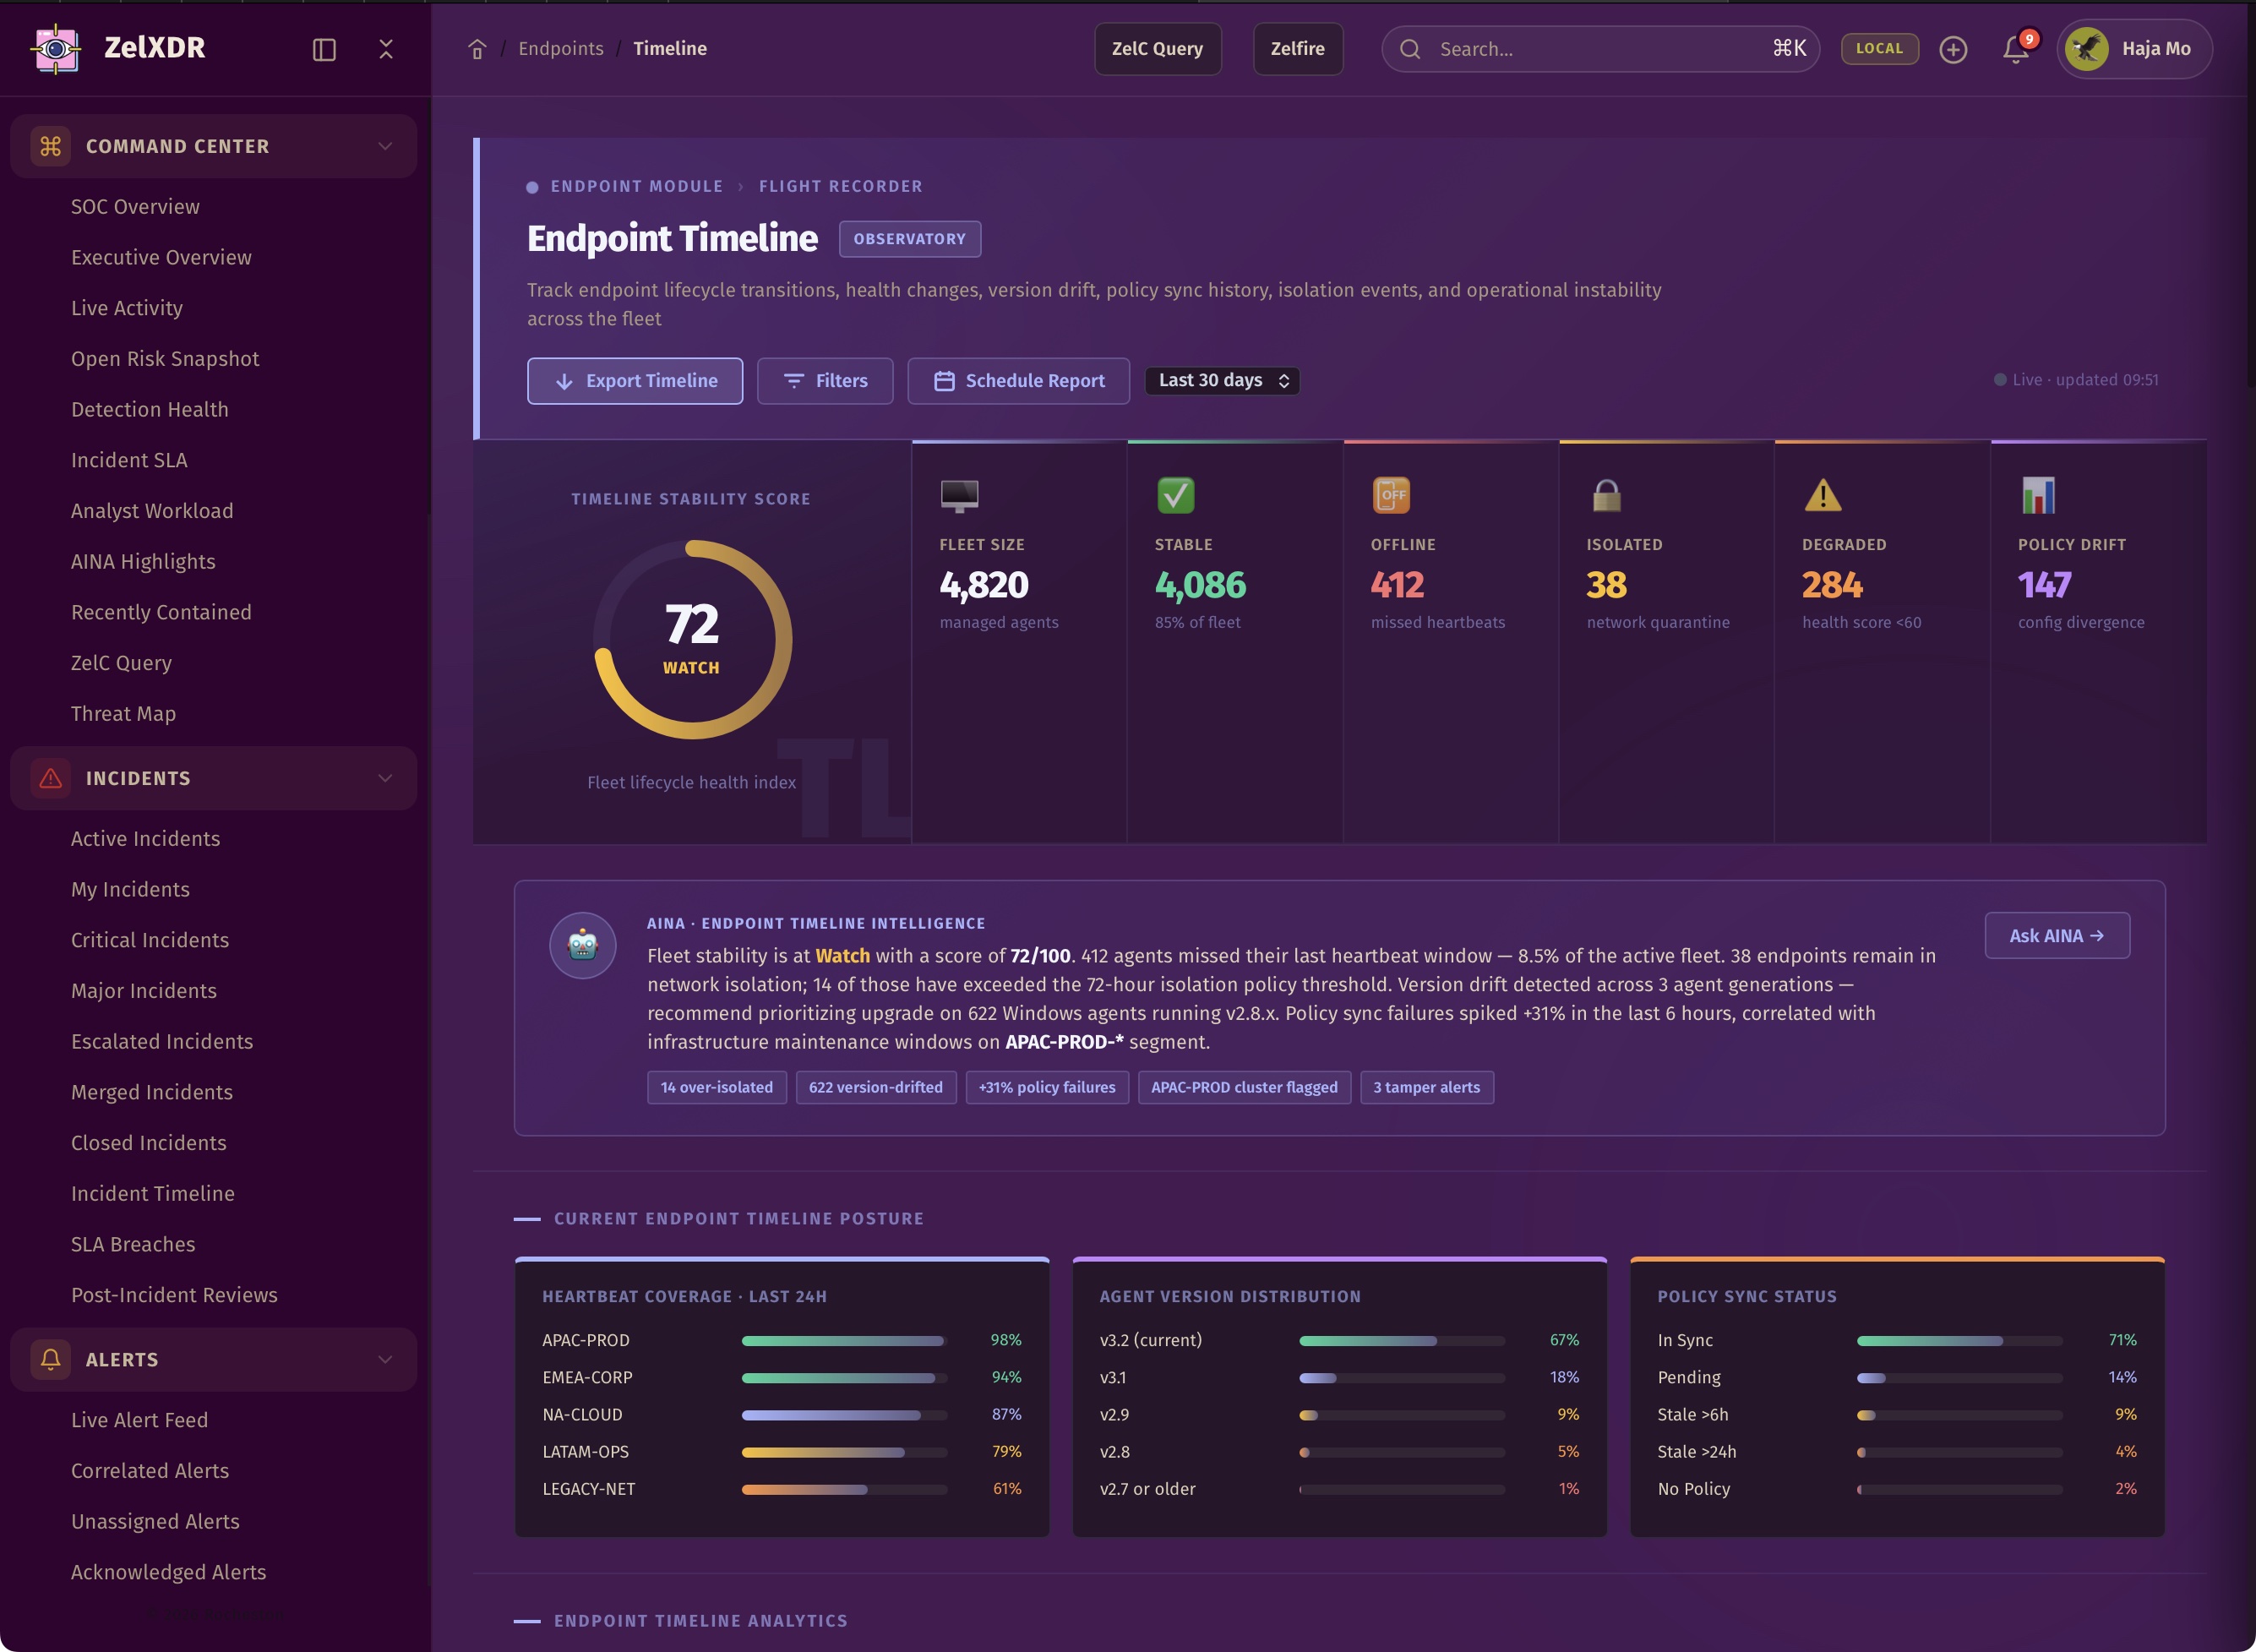
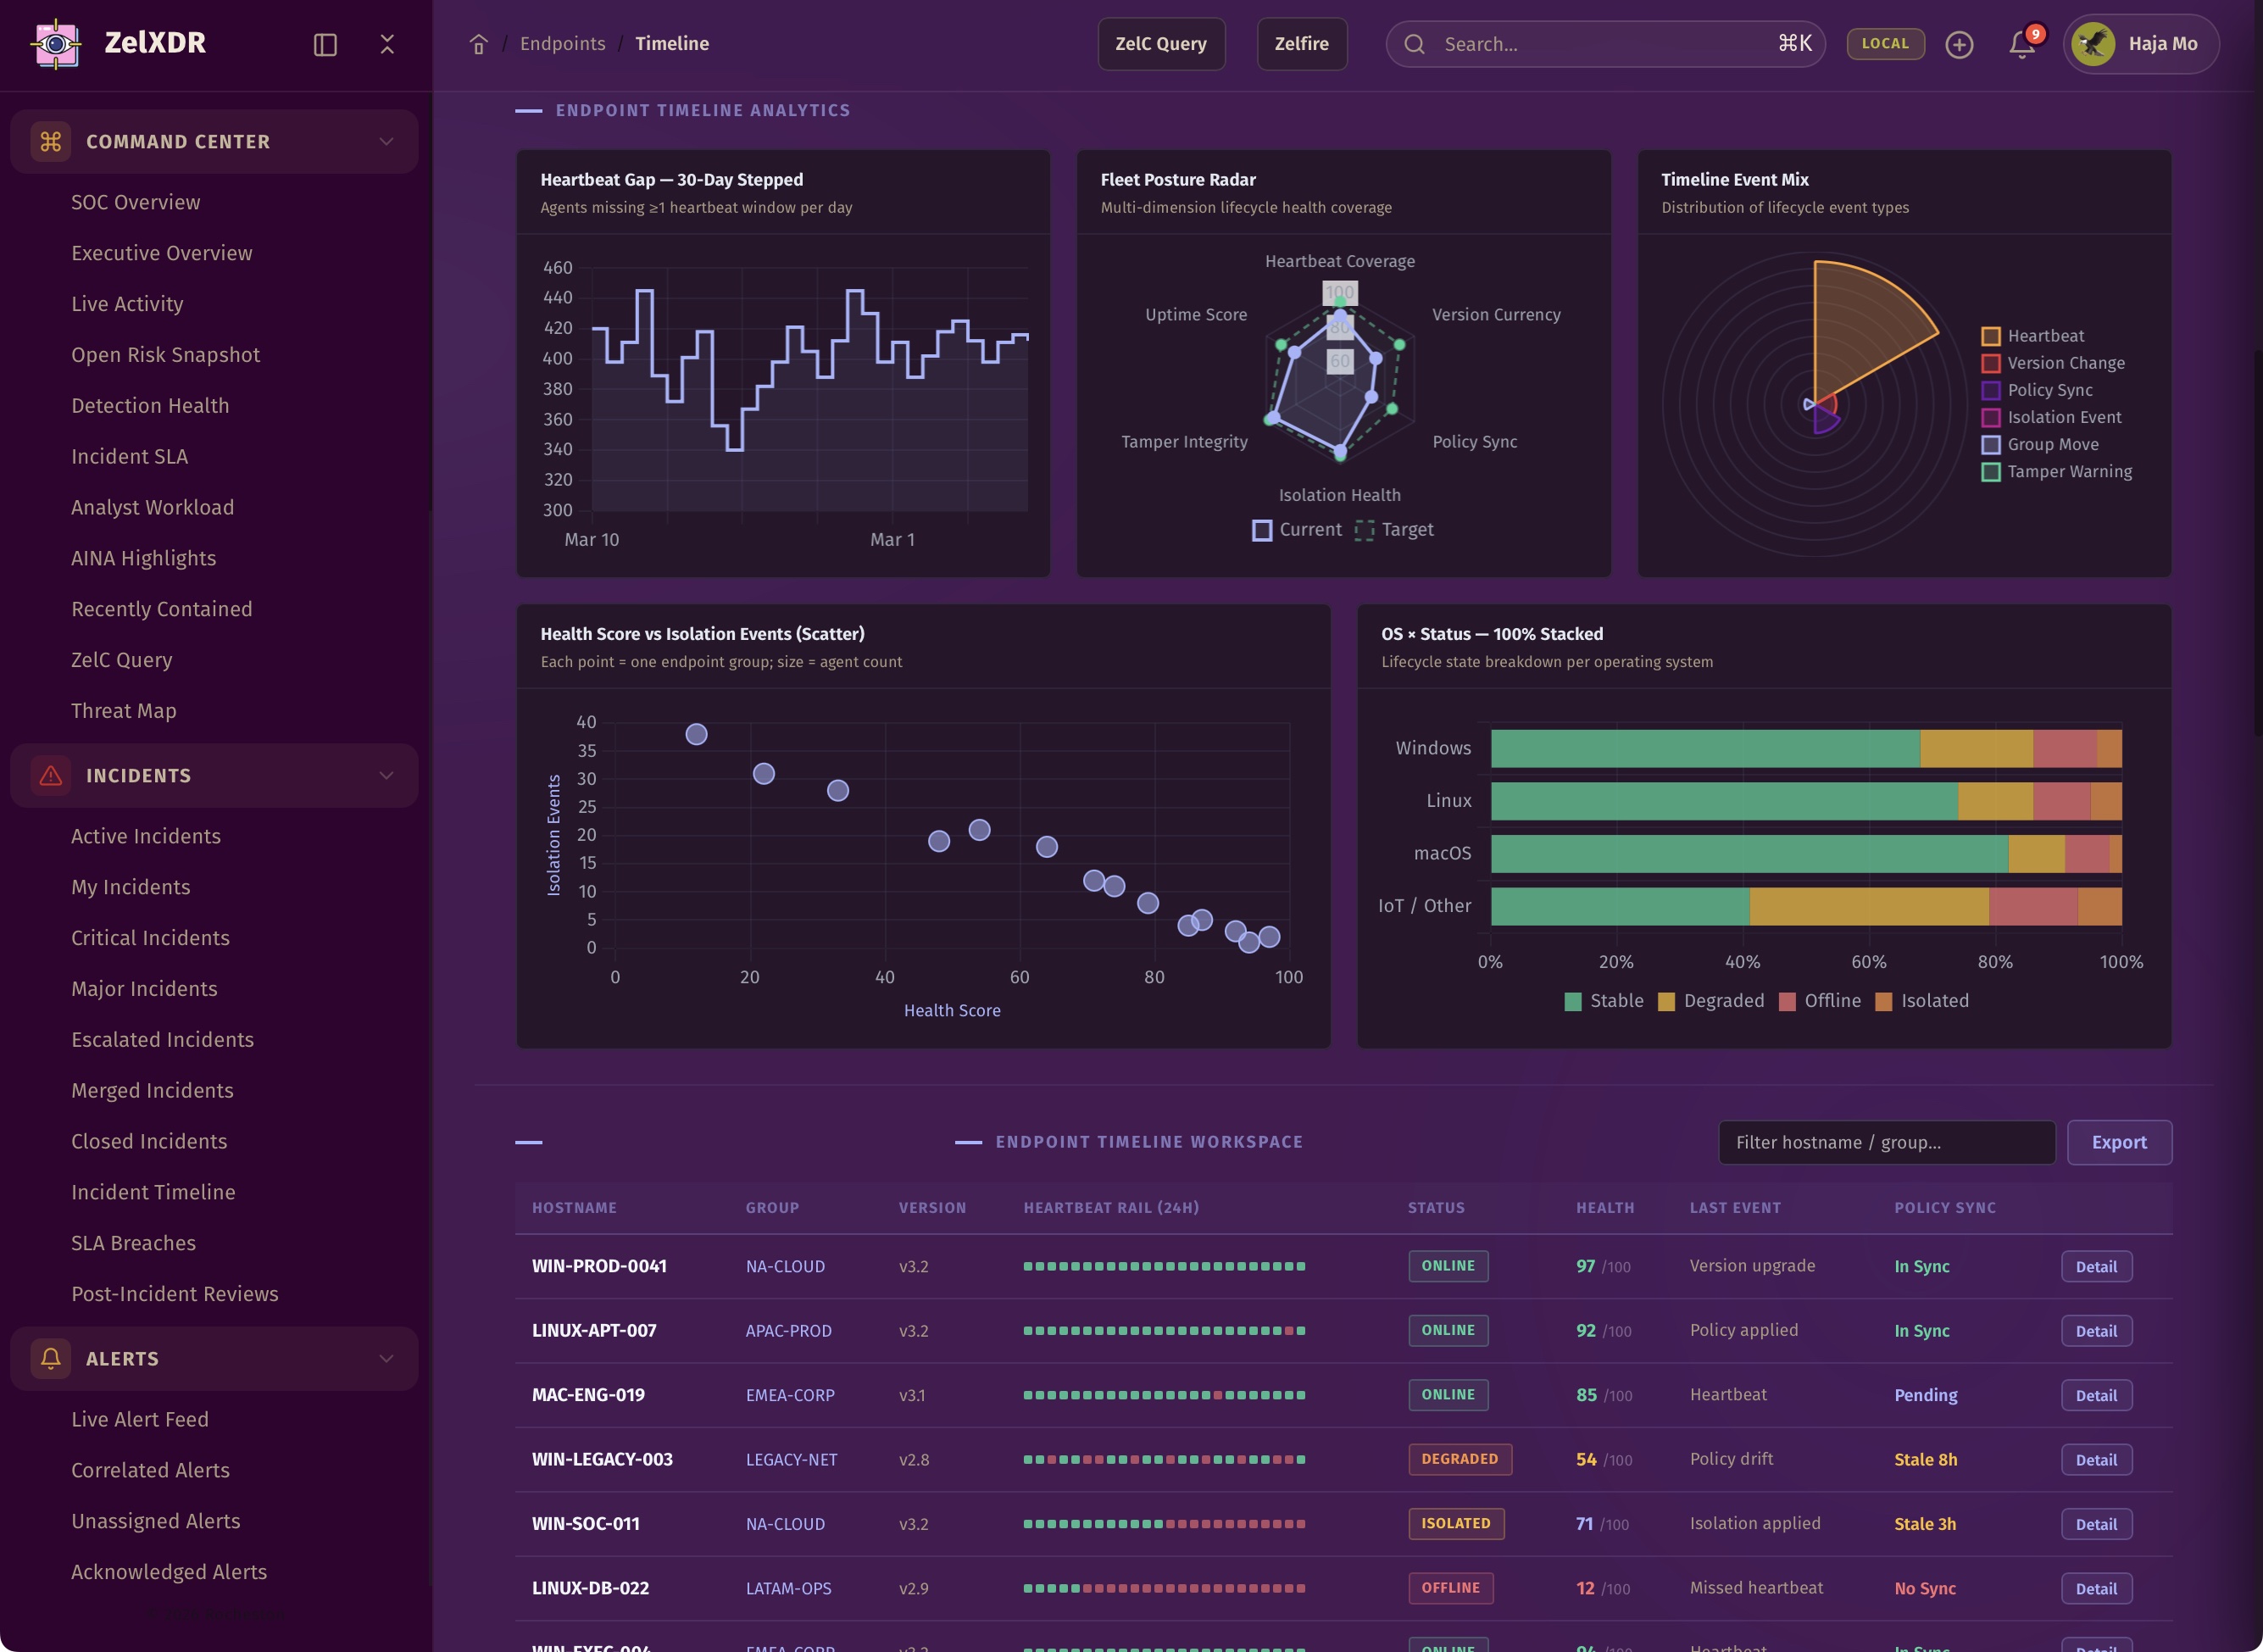
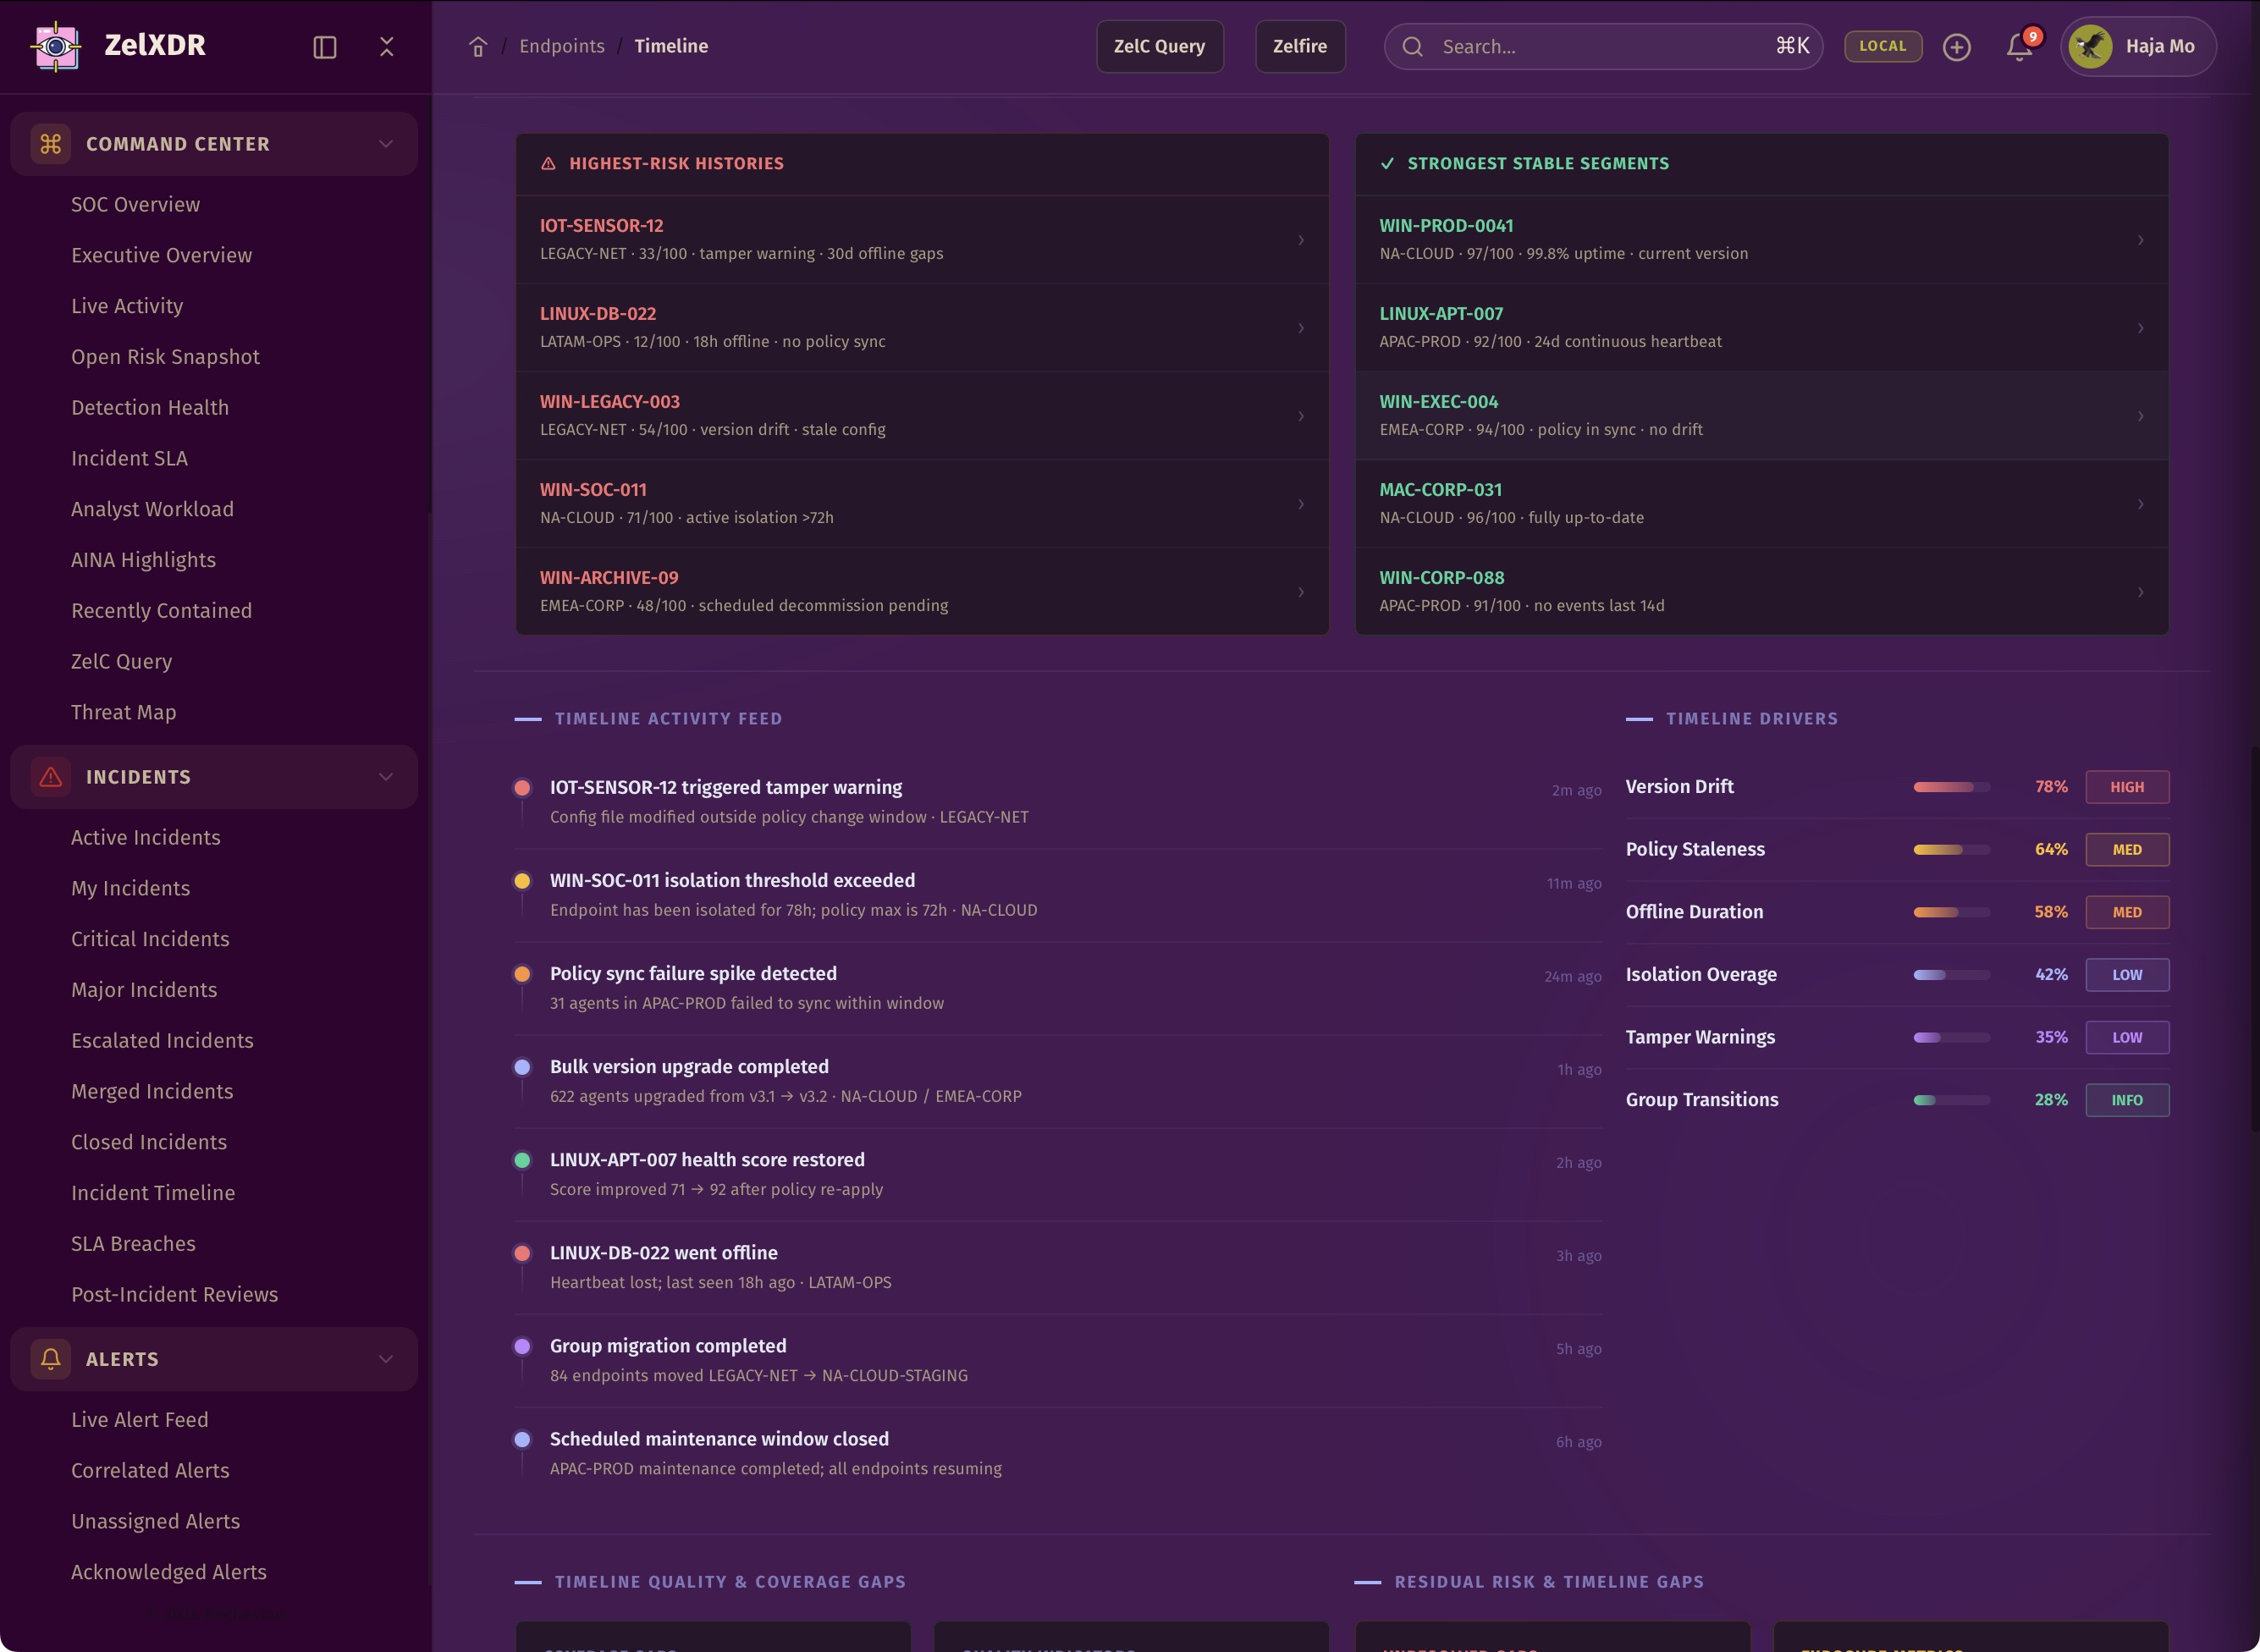
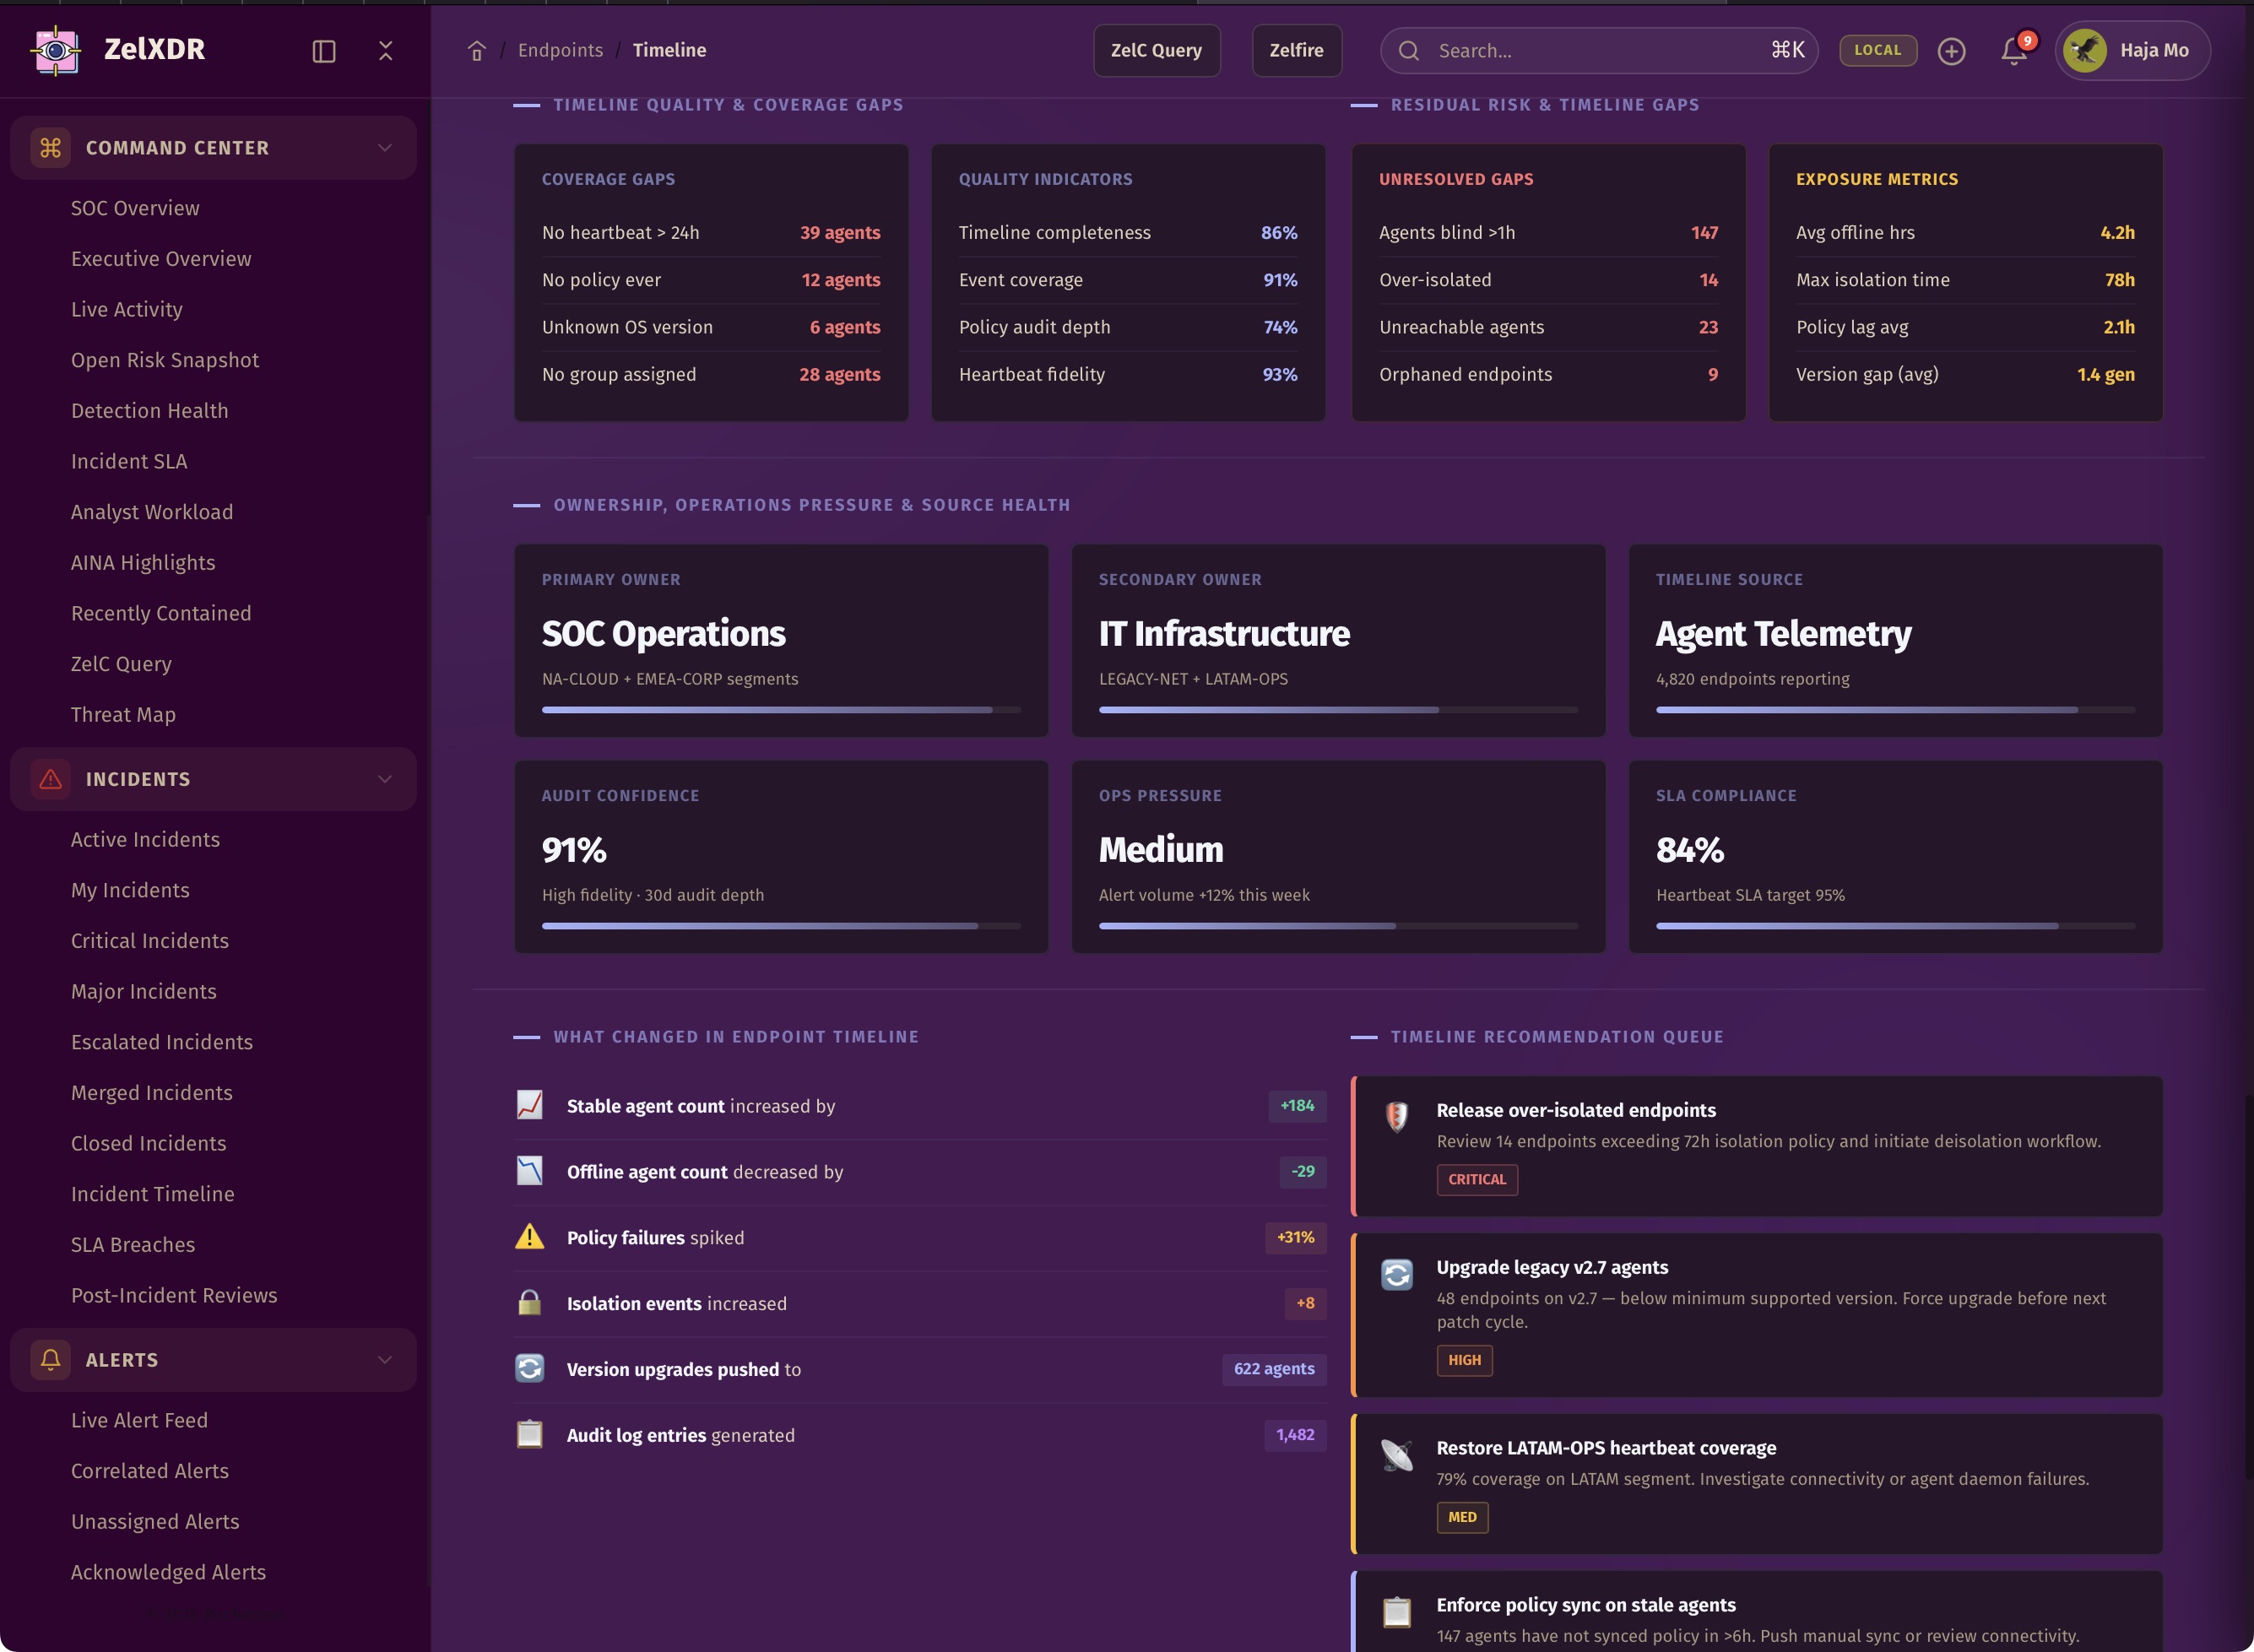
From health and policy state to isolation history and version drift, ZelXDR provides deep endpoint visibility. It helps teams understand which machines are healthy, unstable, exposed, or actively involved in investigations.
Every endpoint has a story. ZelXDR helps you read it.
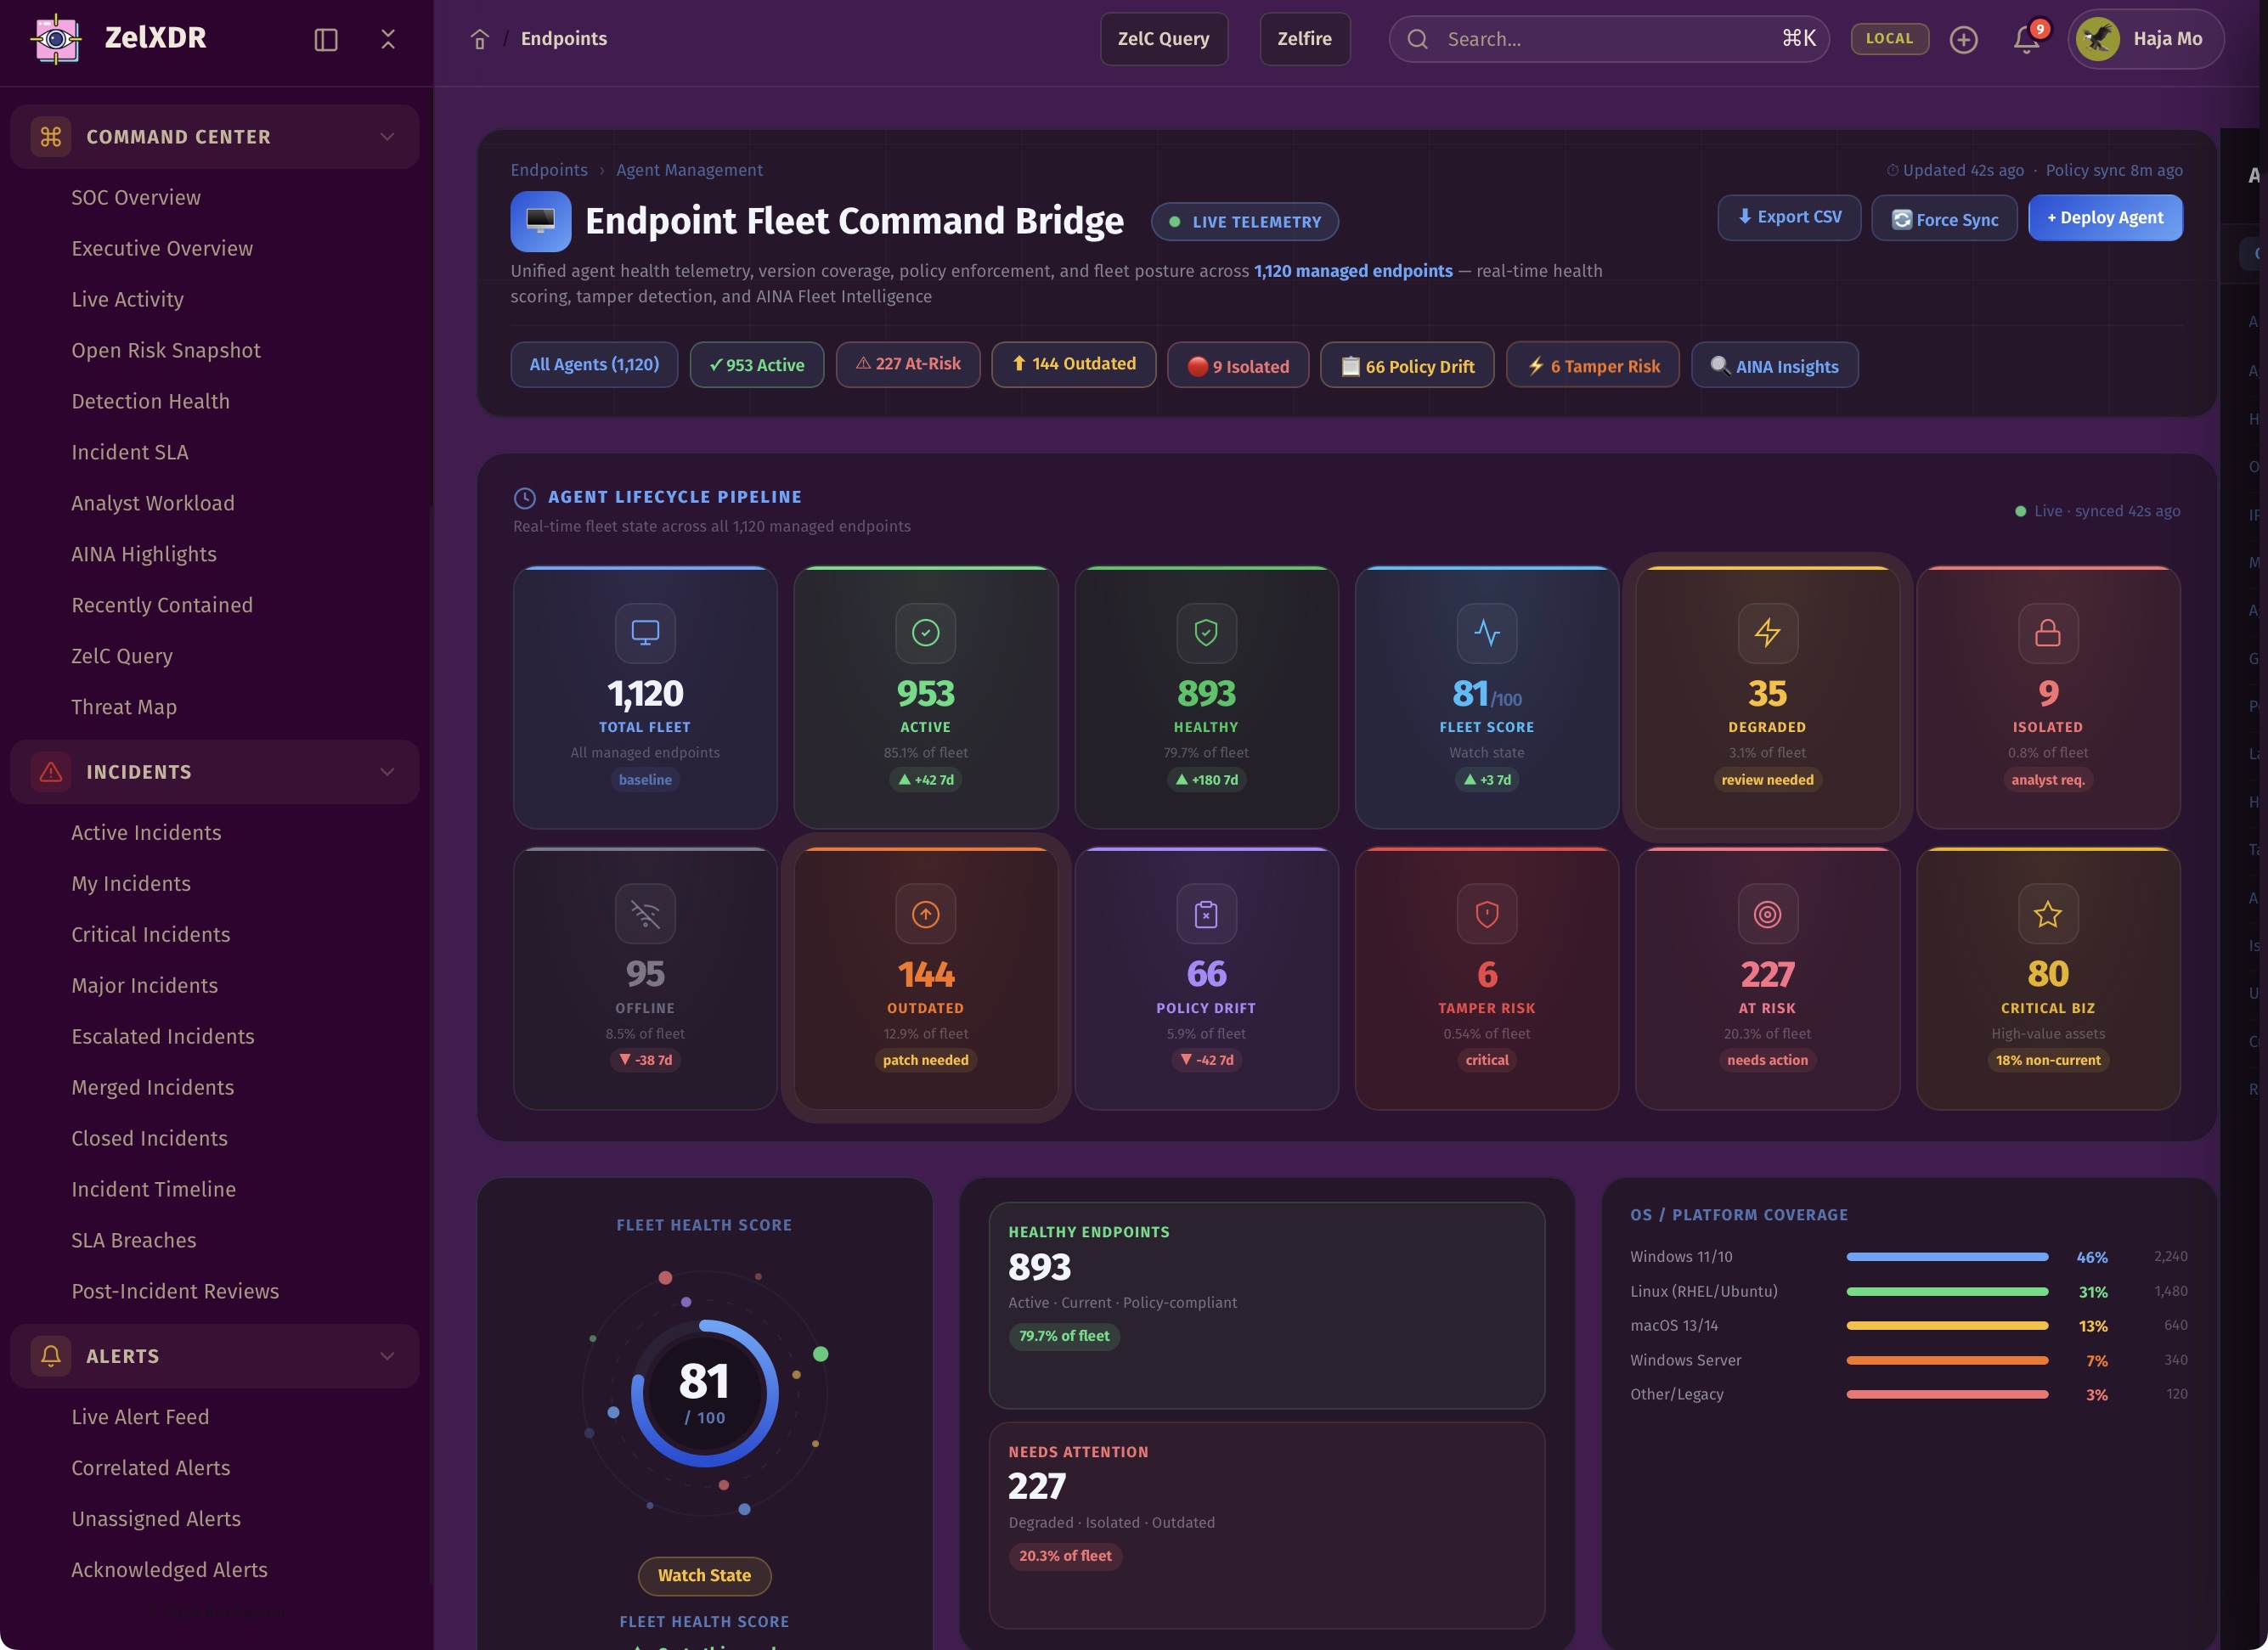
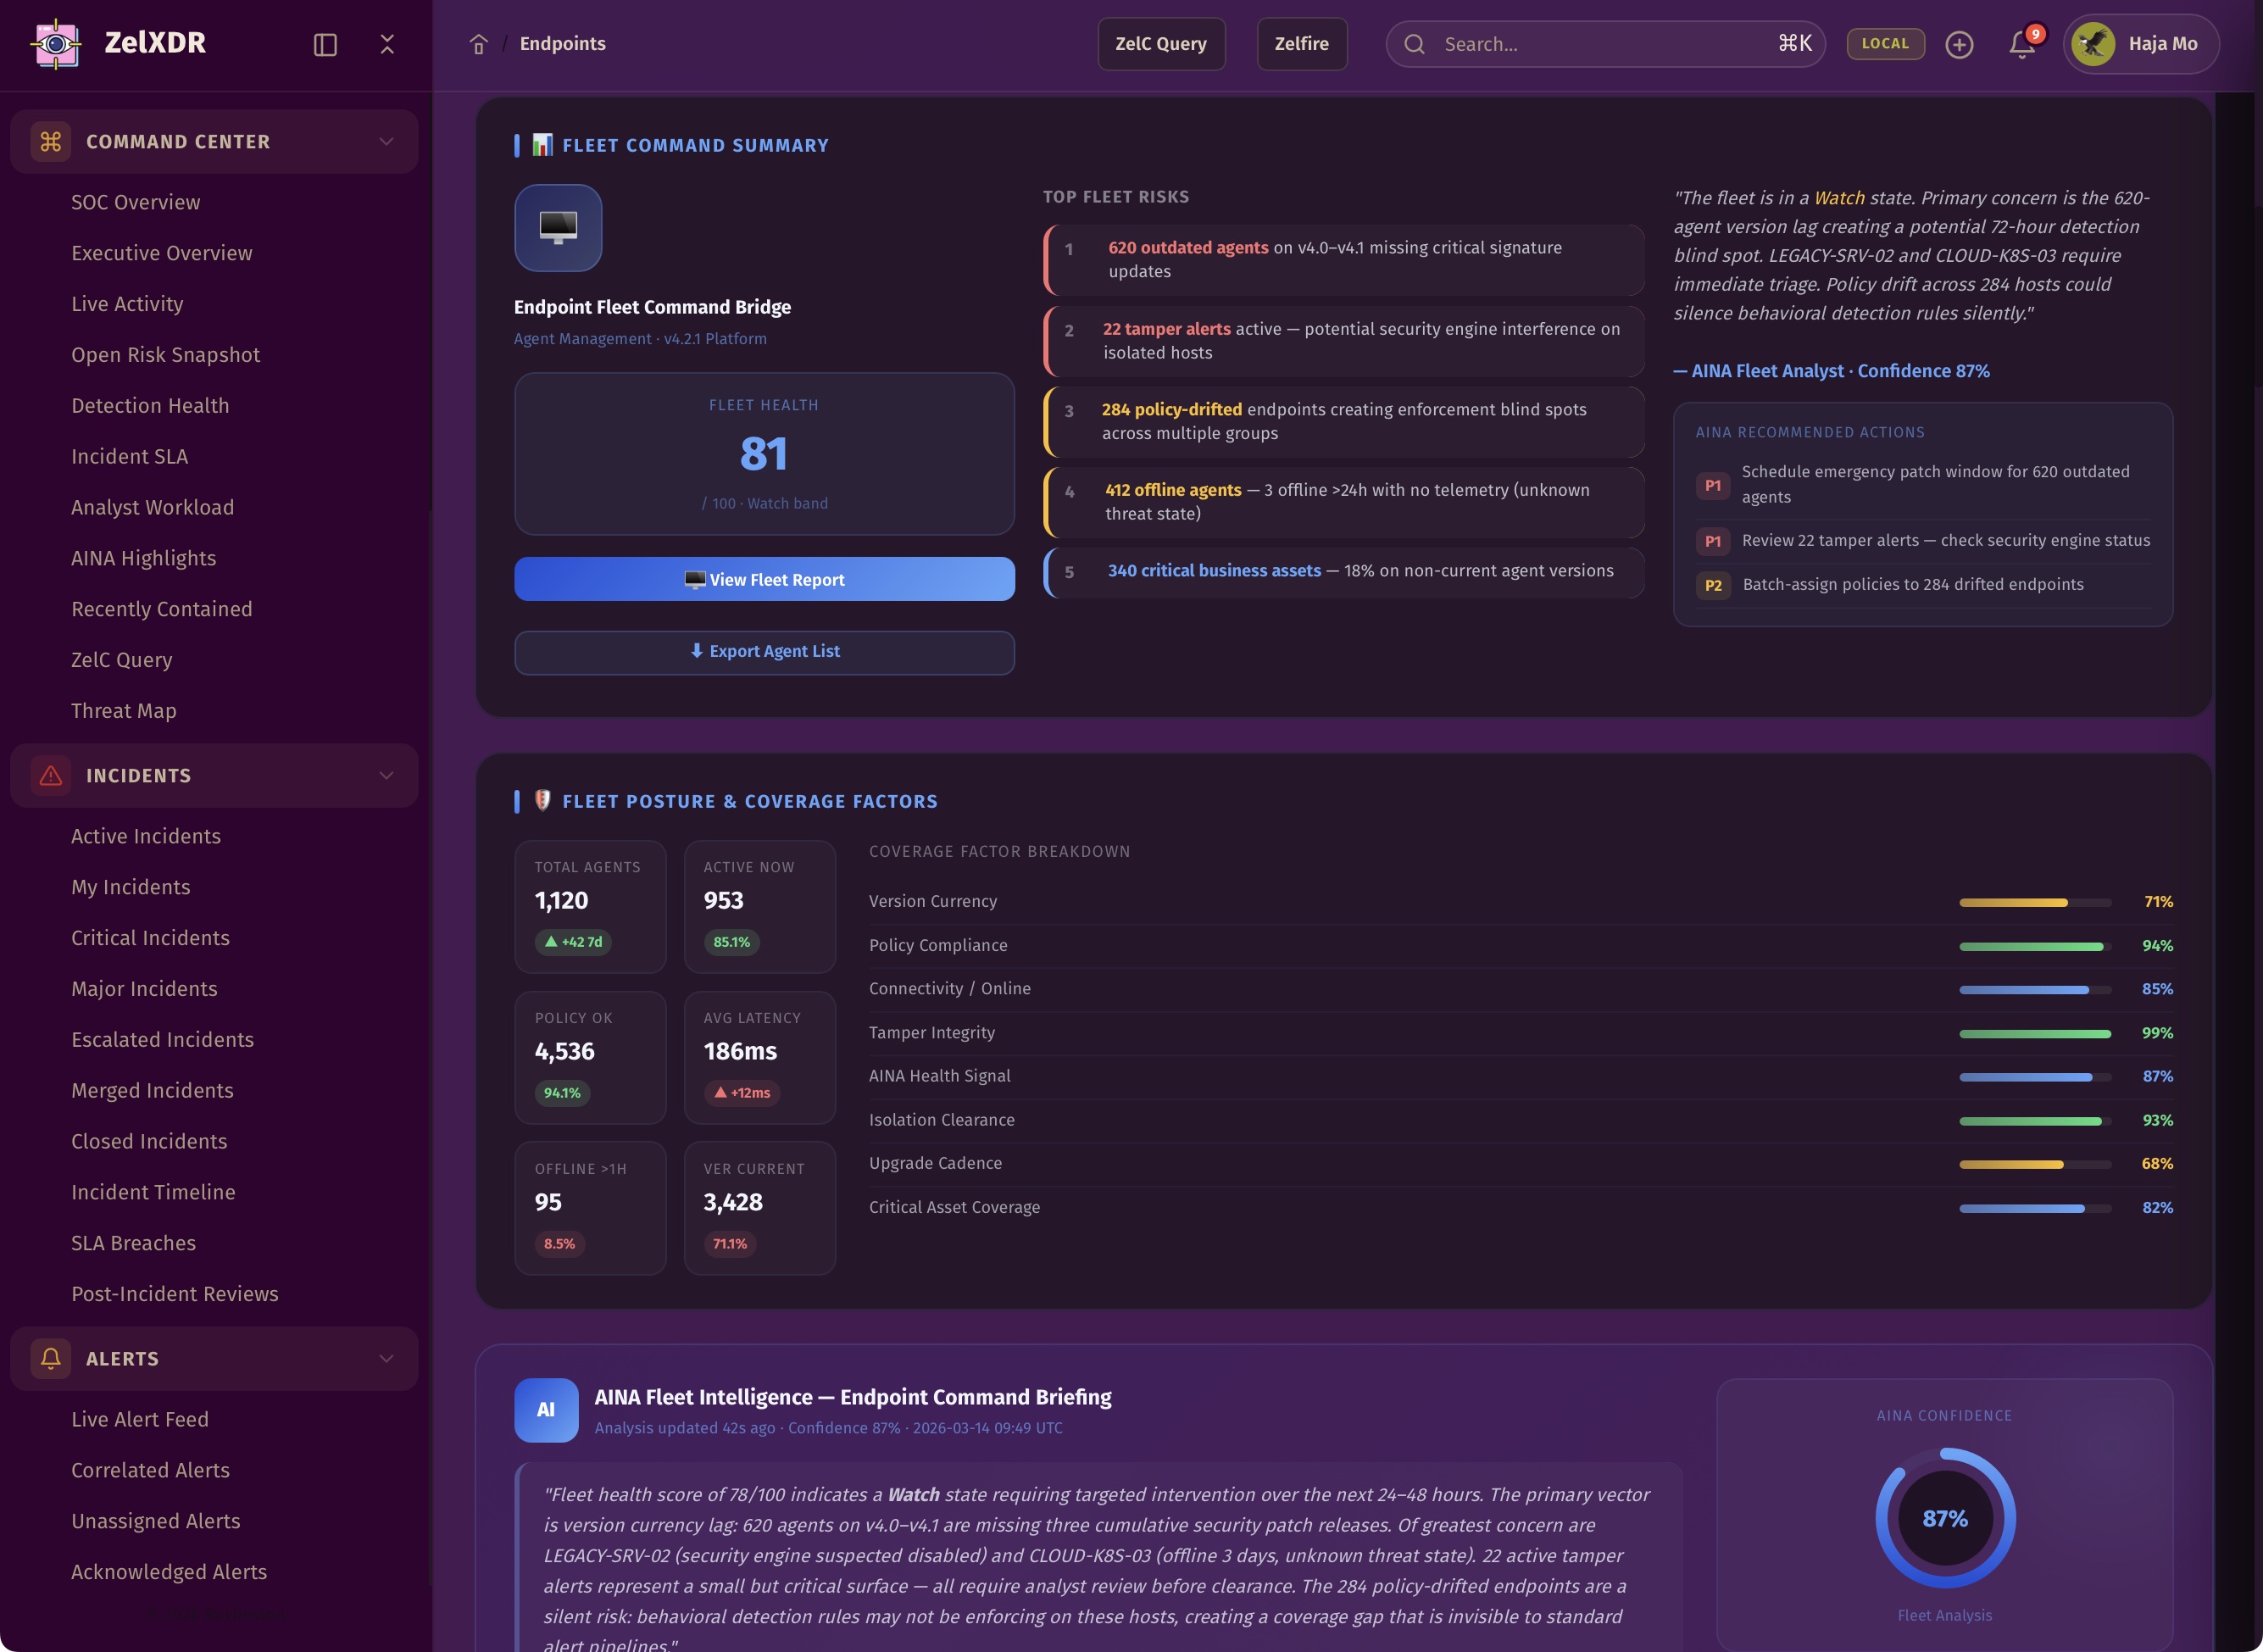
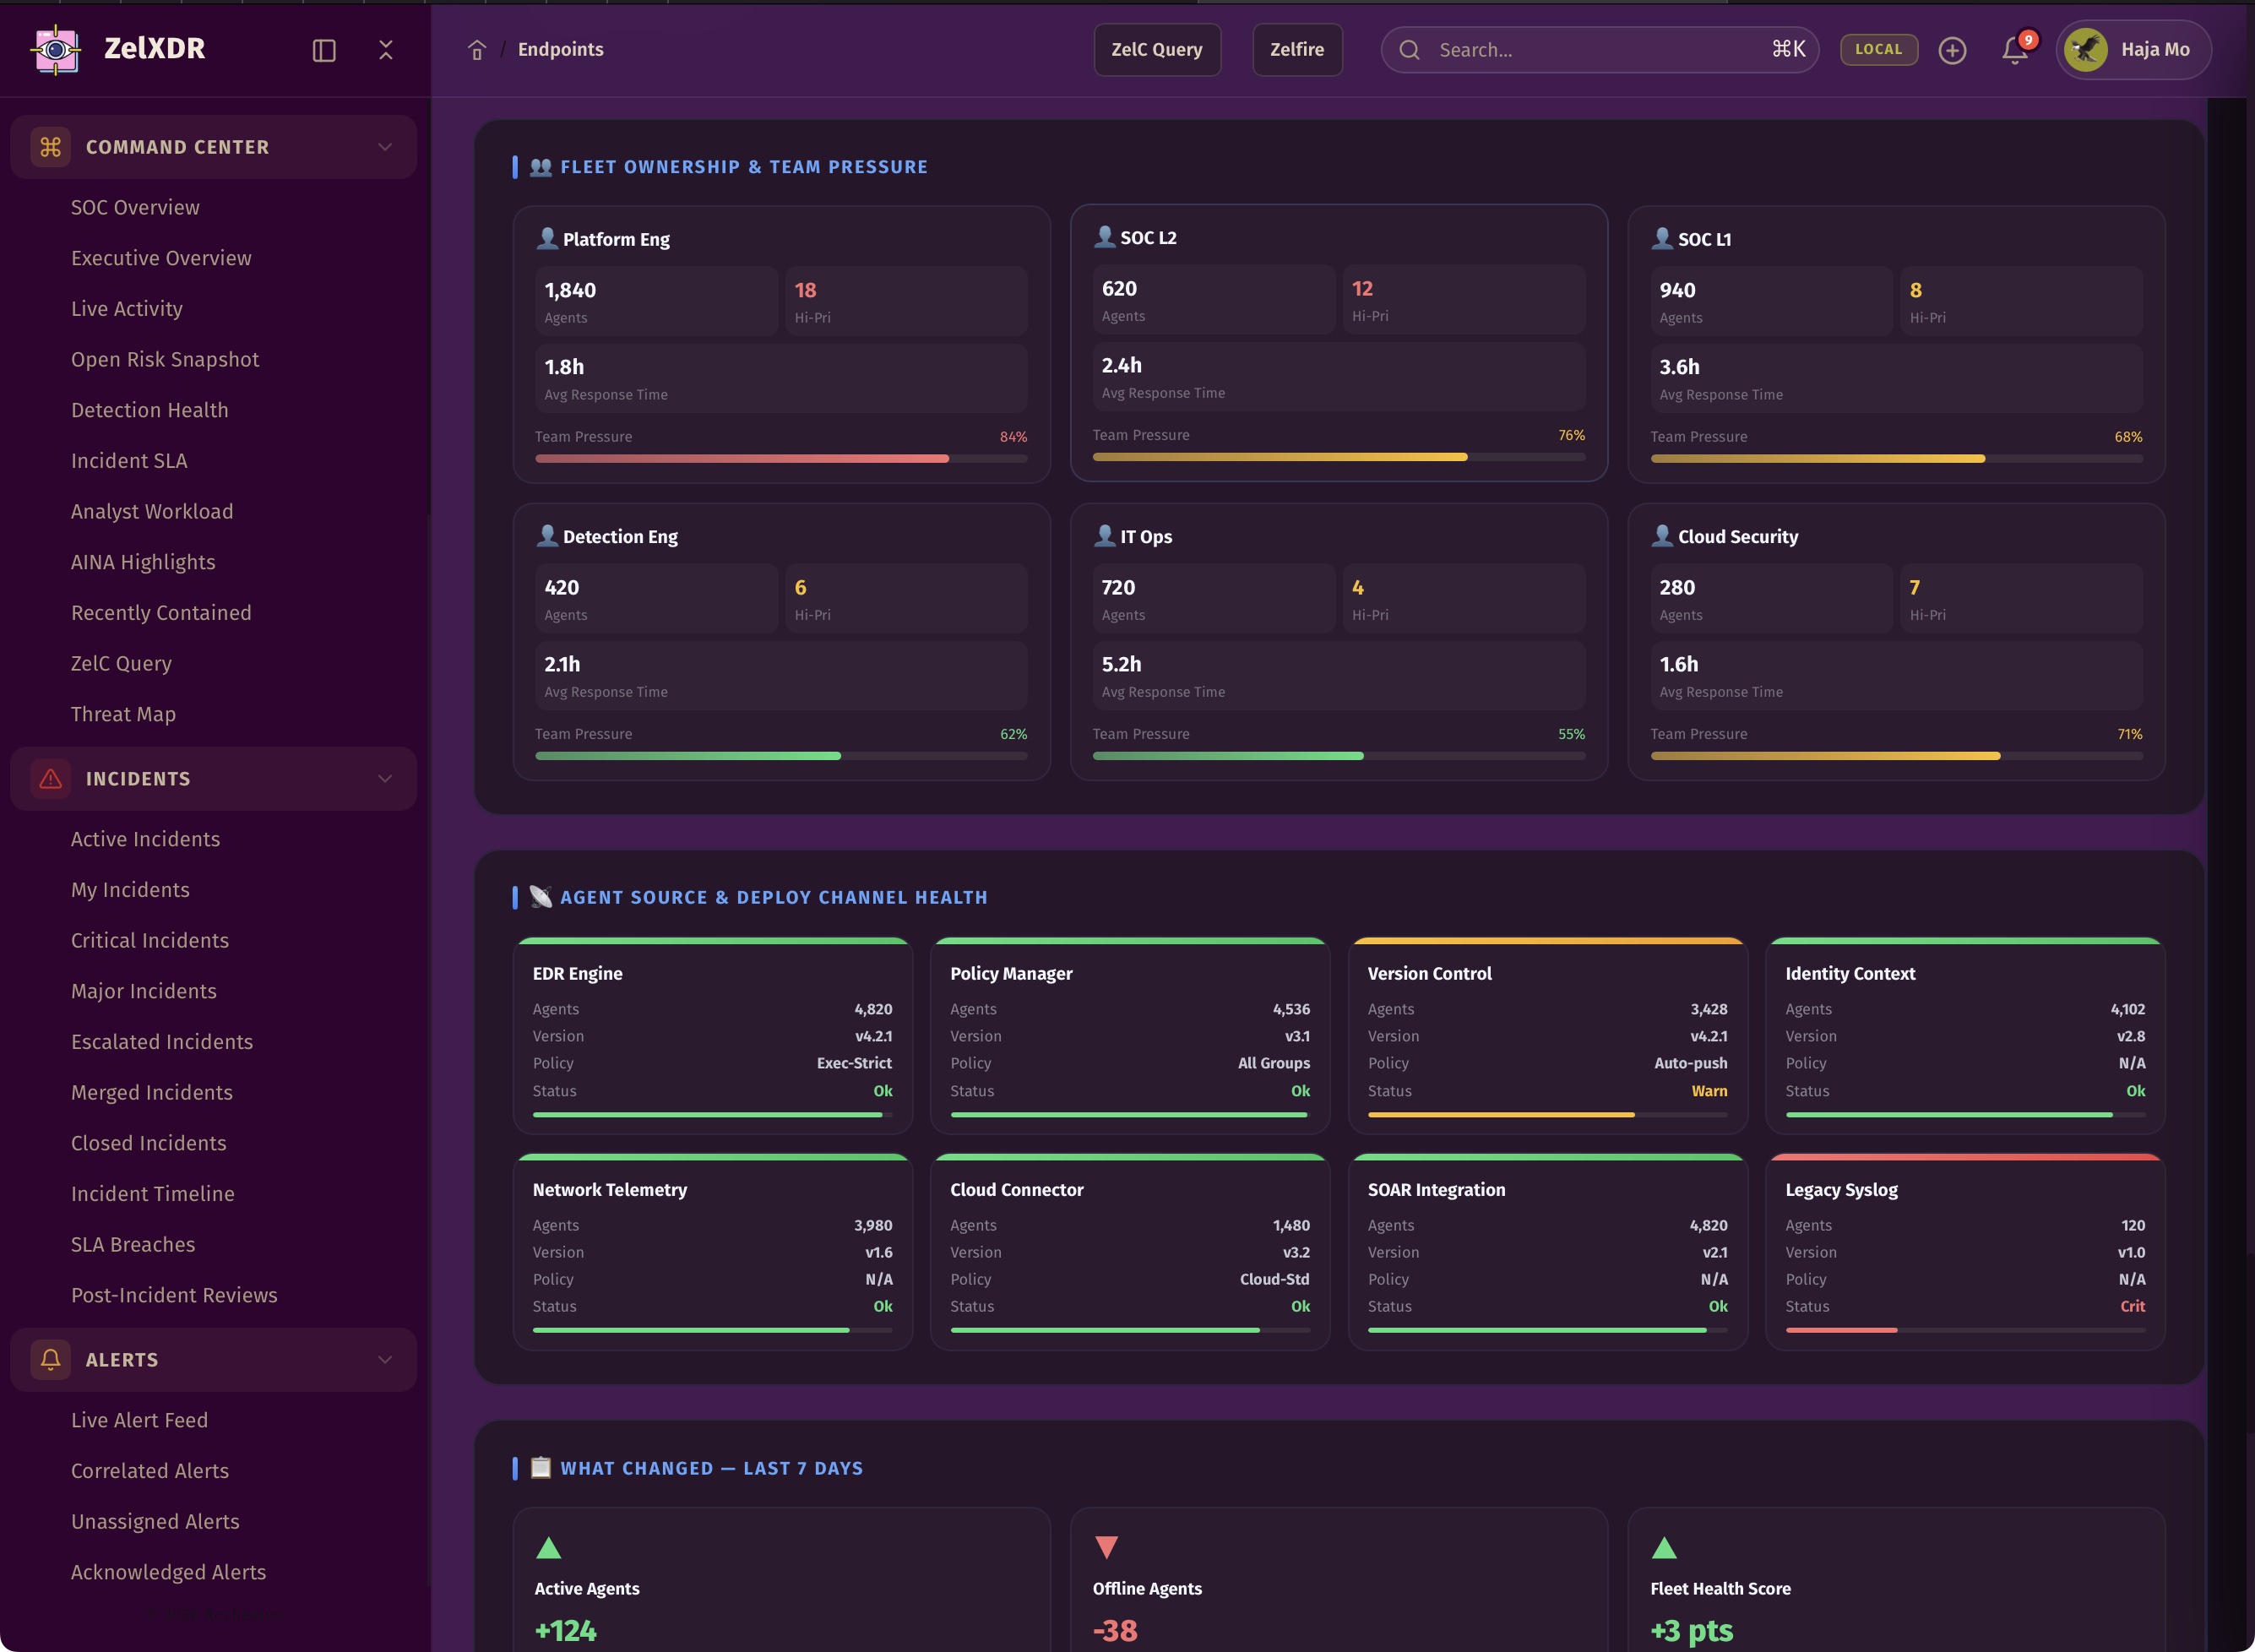
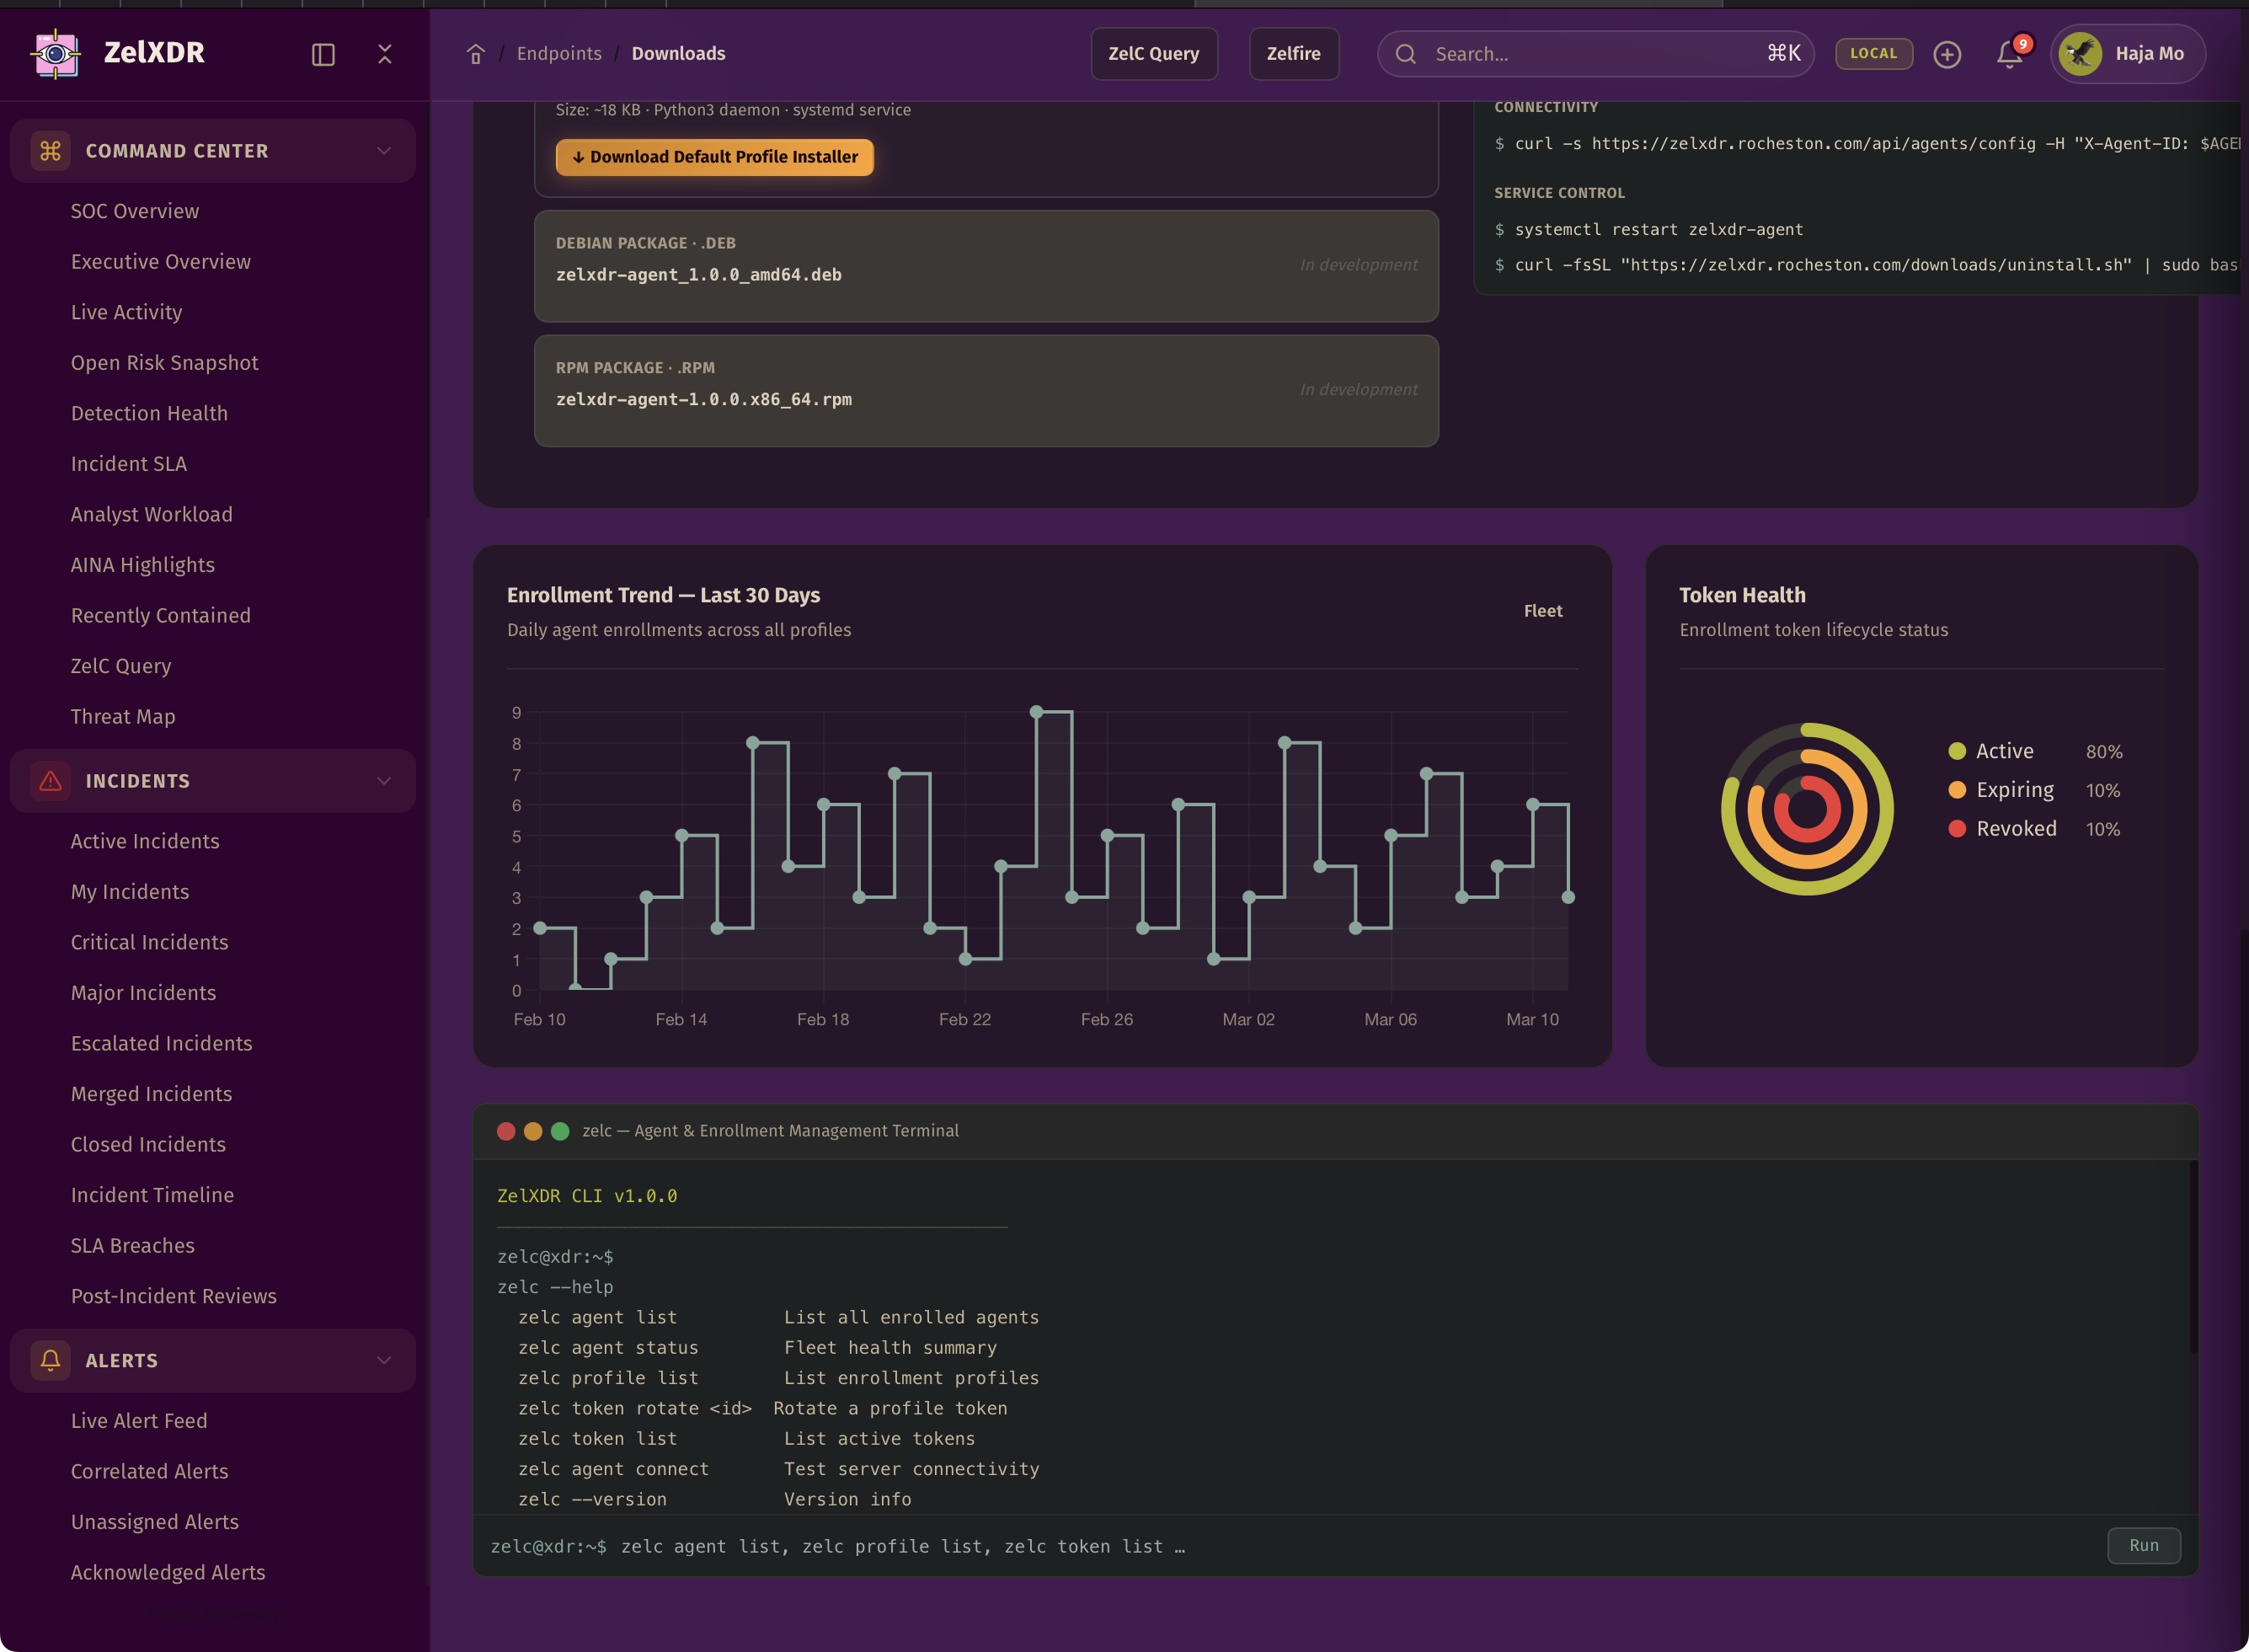
ZelXDR makes it easy to manage large endpoint fleets through enrollment, grouping, updates, policy sync, isolation, and health monitoring. It turns agent operations into a controlled, visible process.
A strong fleet starts with disciplined visibility.
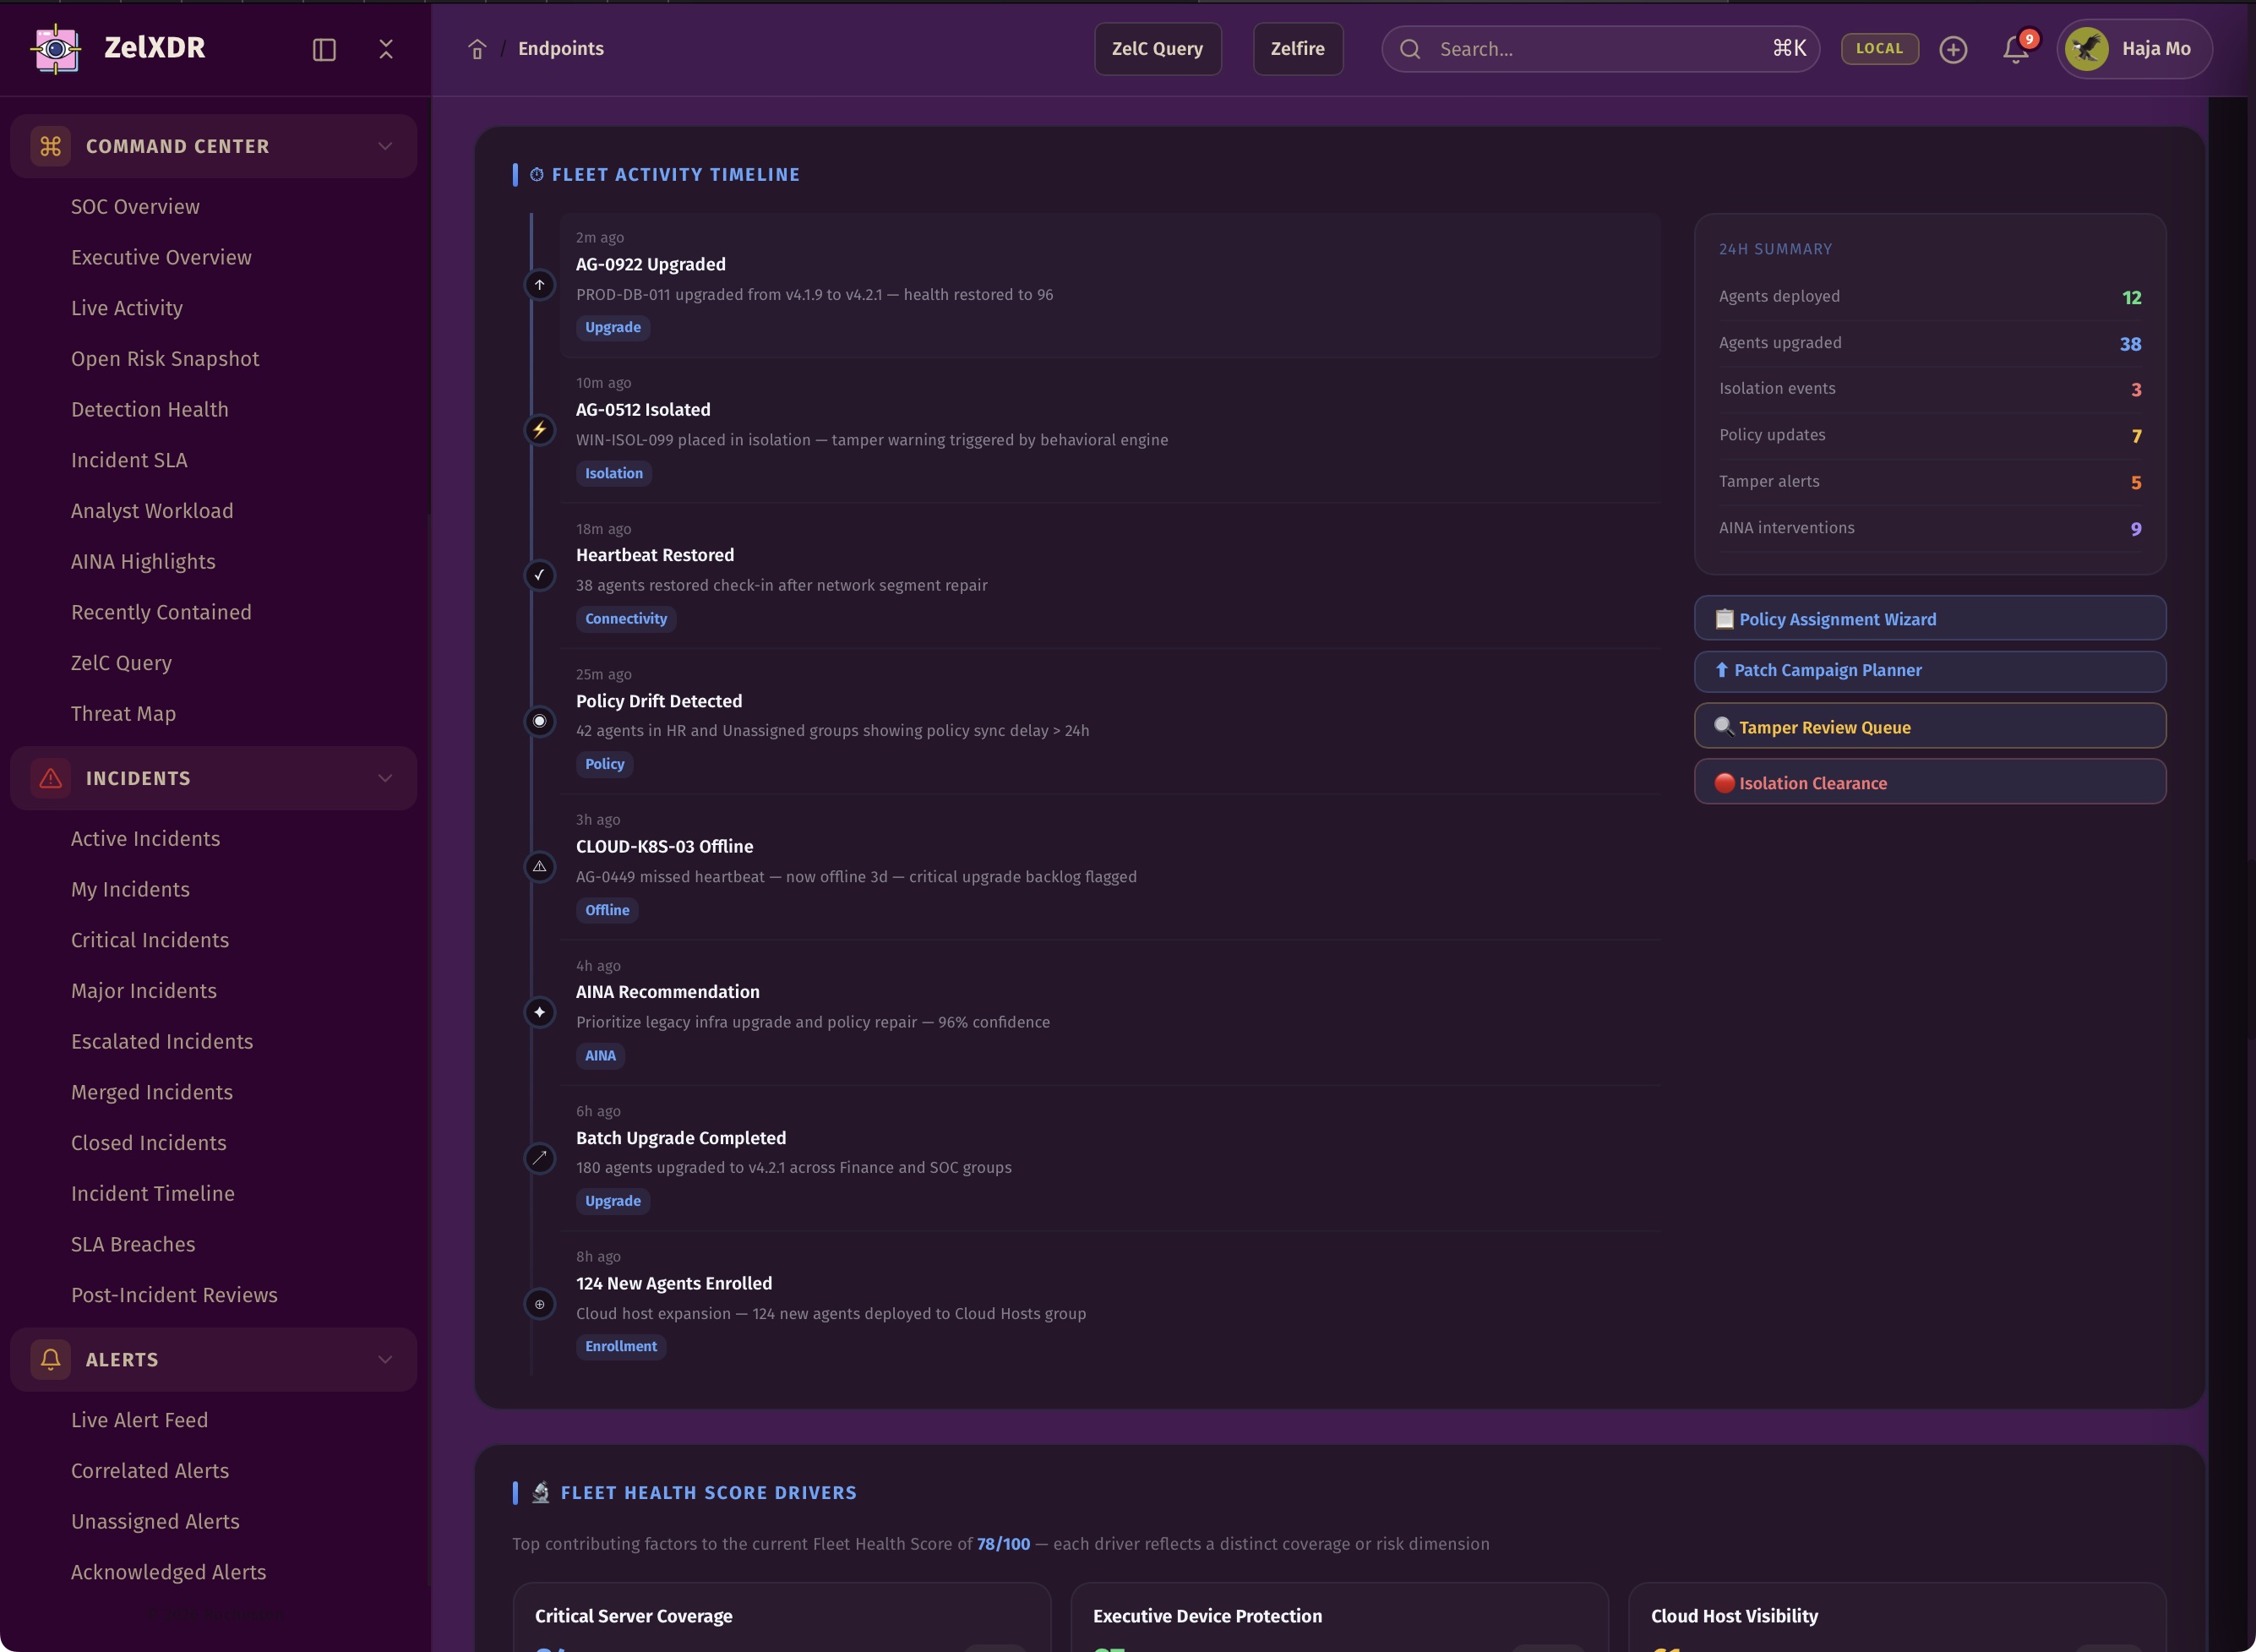
ZelXDR tracks heartbeat changes, policy updates, isolation actions, upgrades, tamper events, and operational transitions across endpoints. This makes lifecycle history visible and investigation-ready.
Endpoint history reveals patterns that snapshots miss.
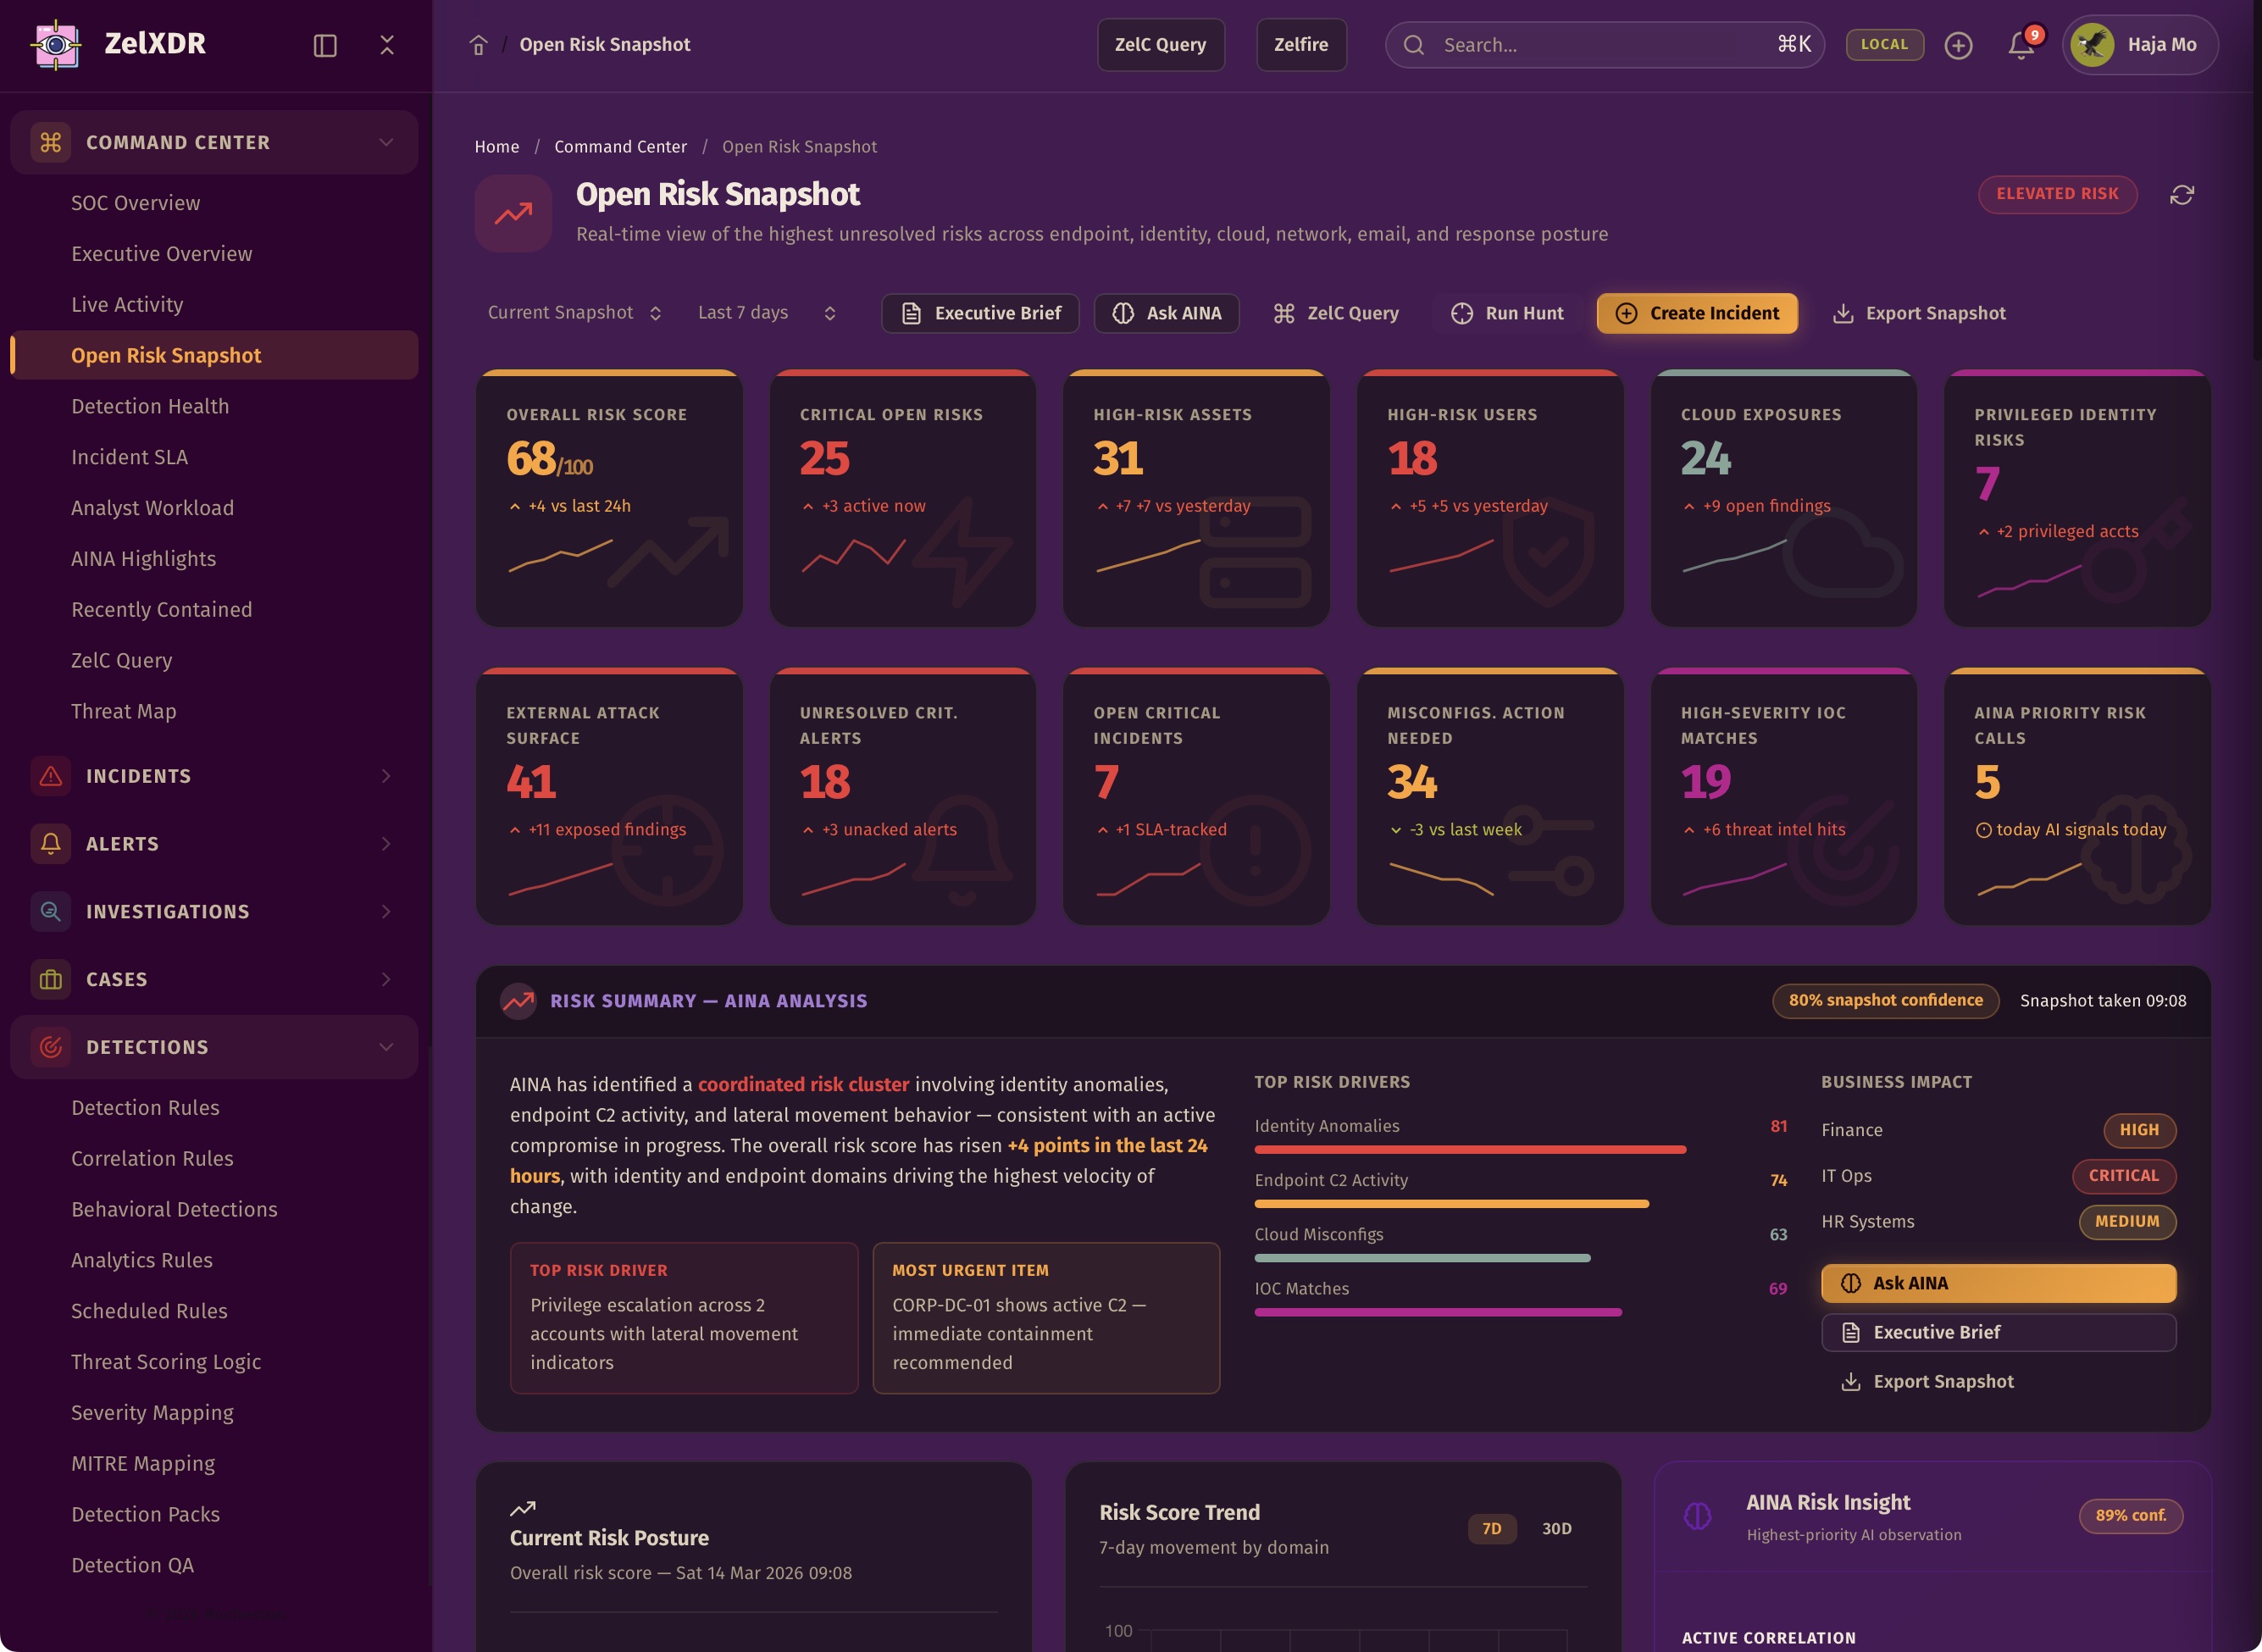
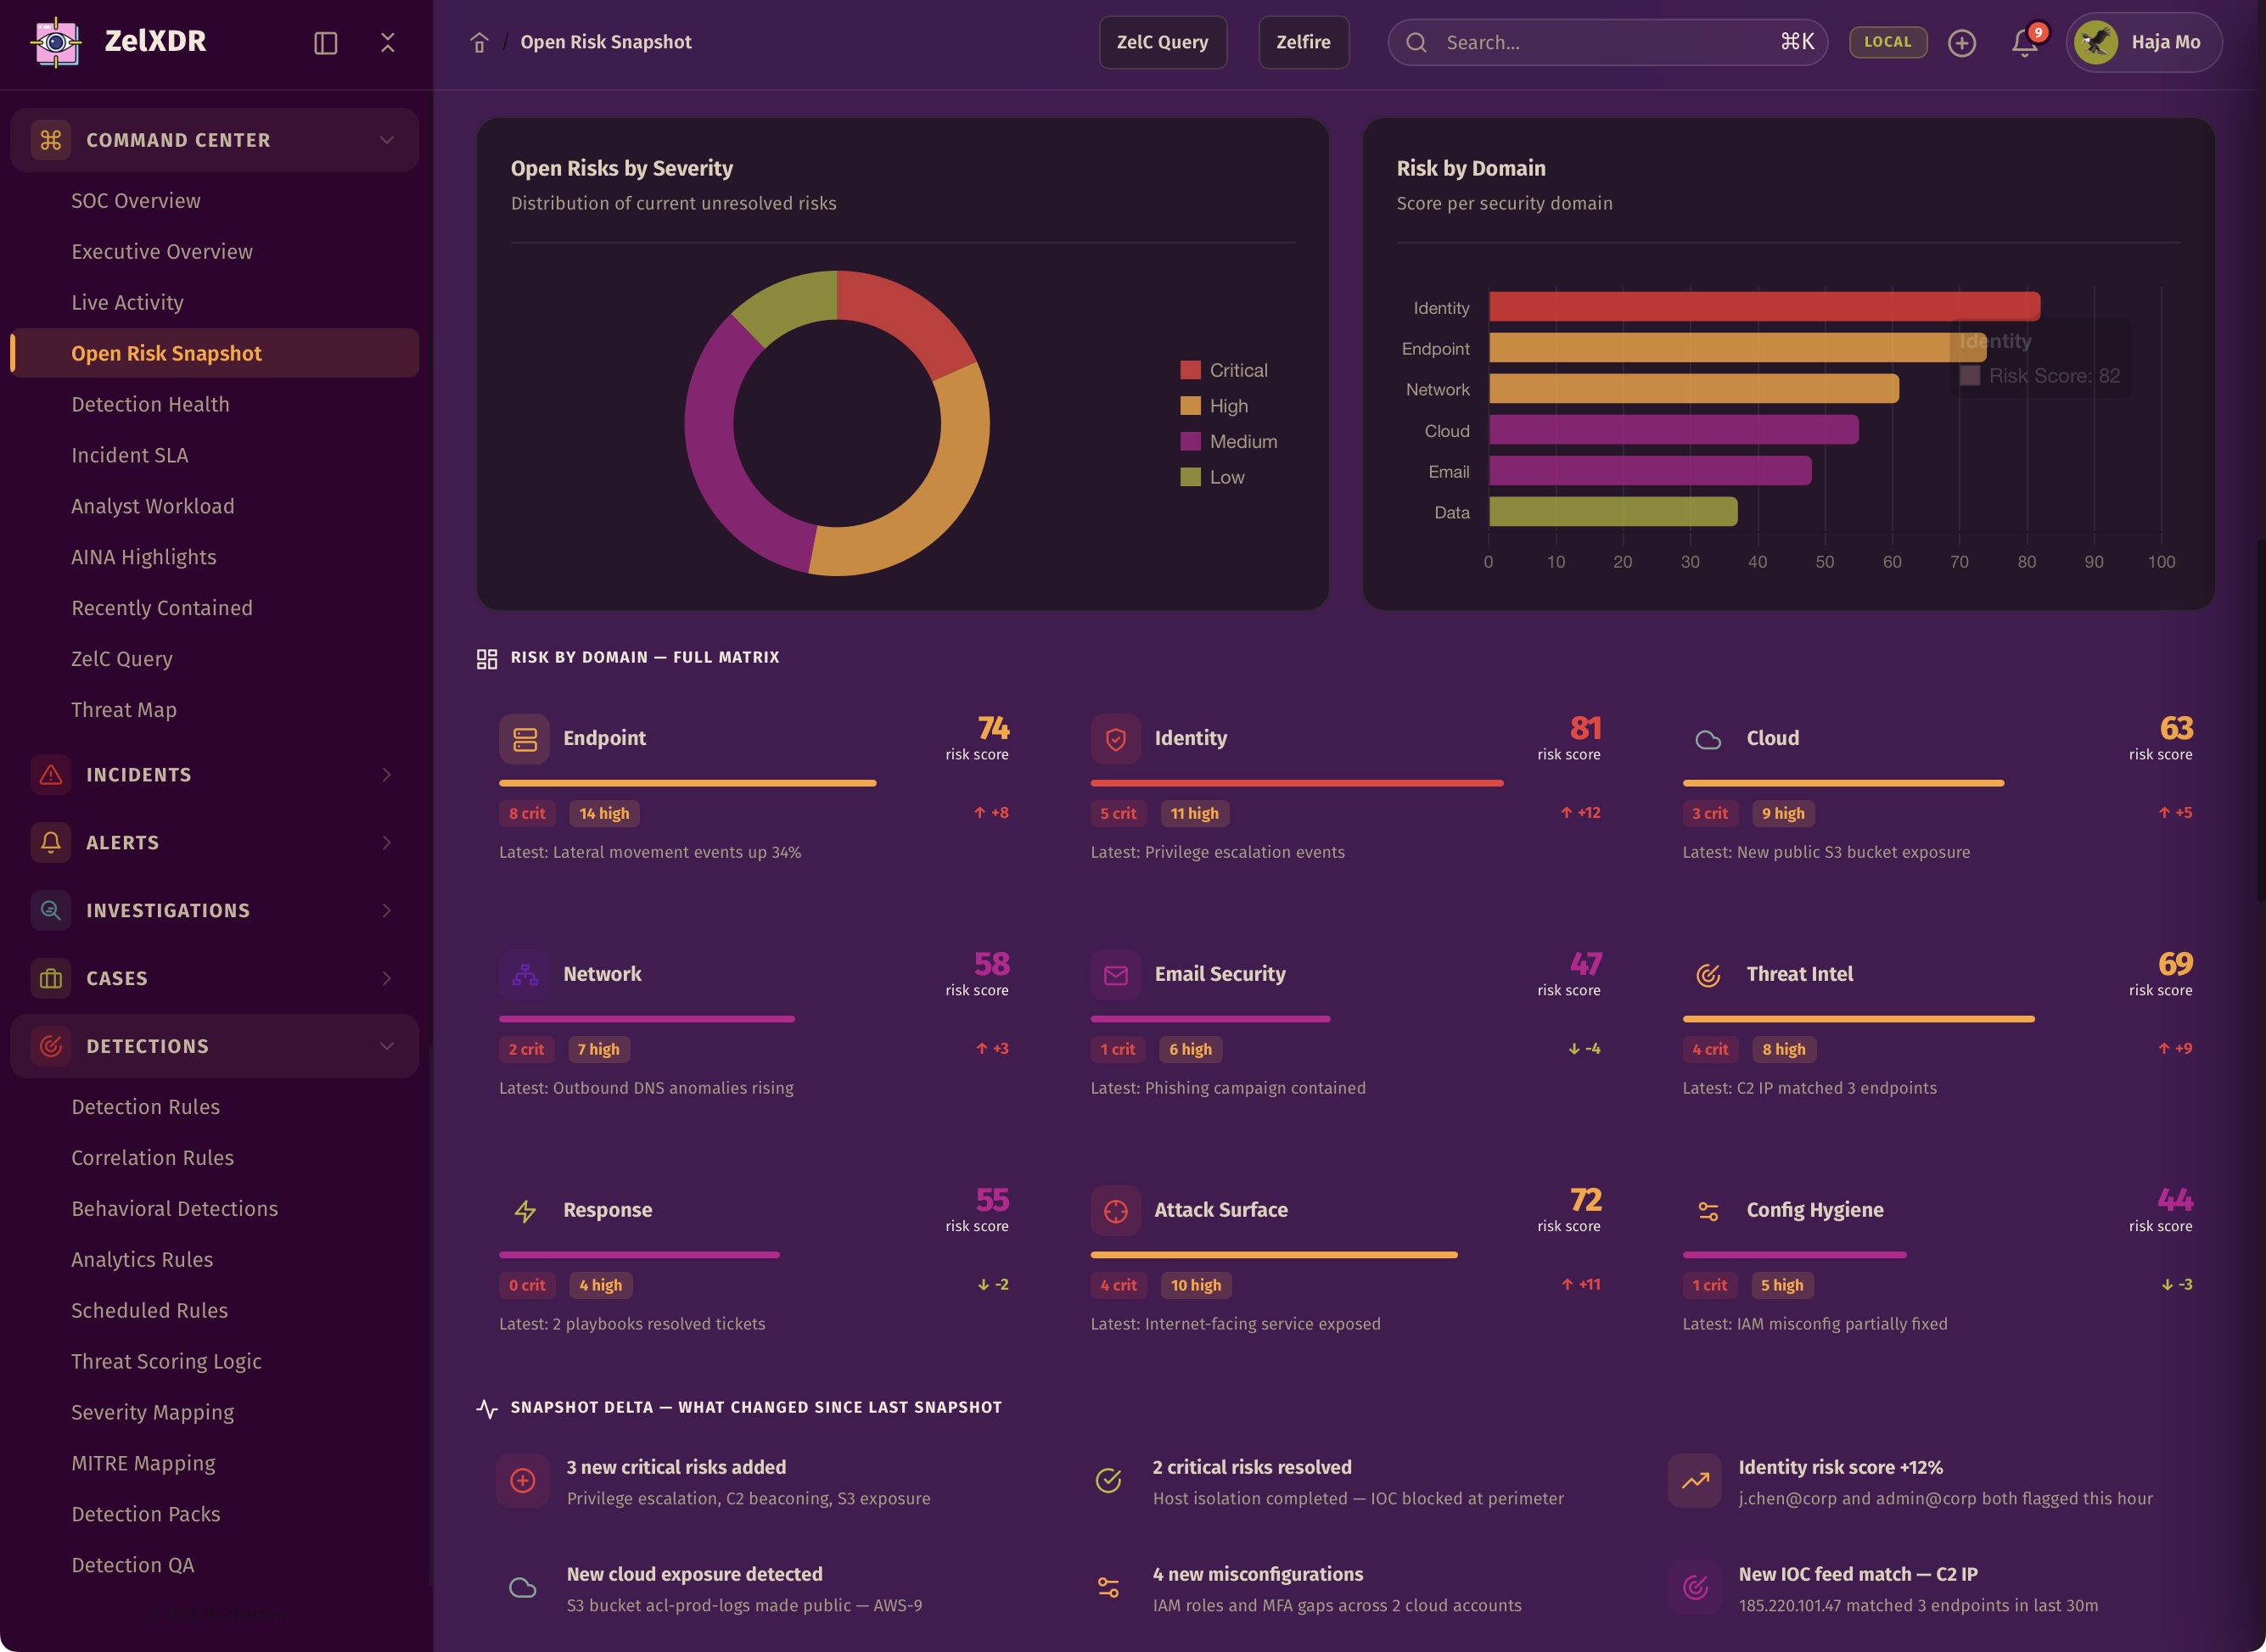
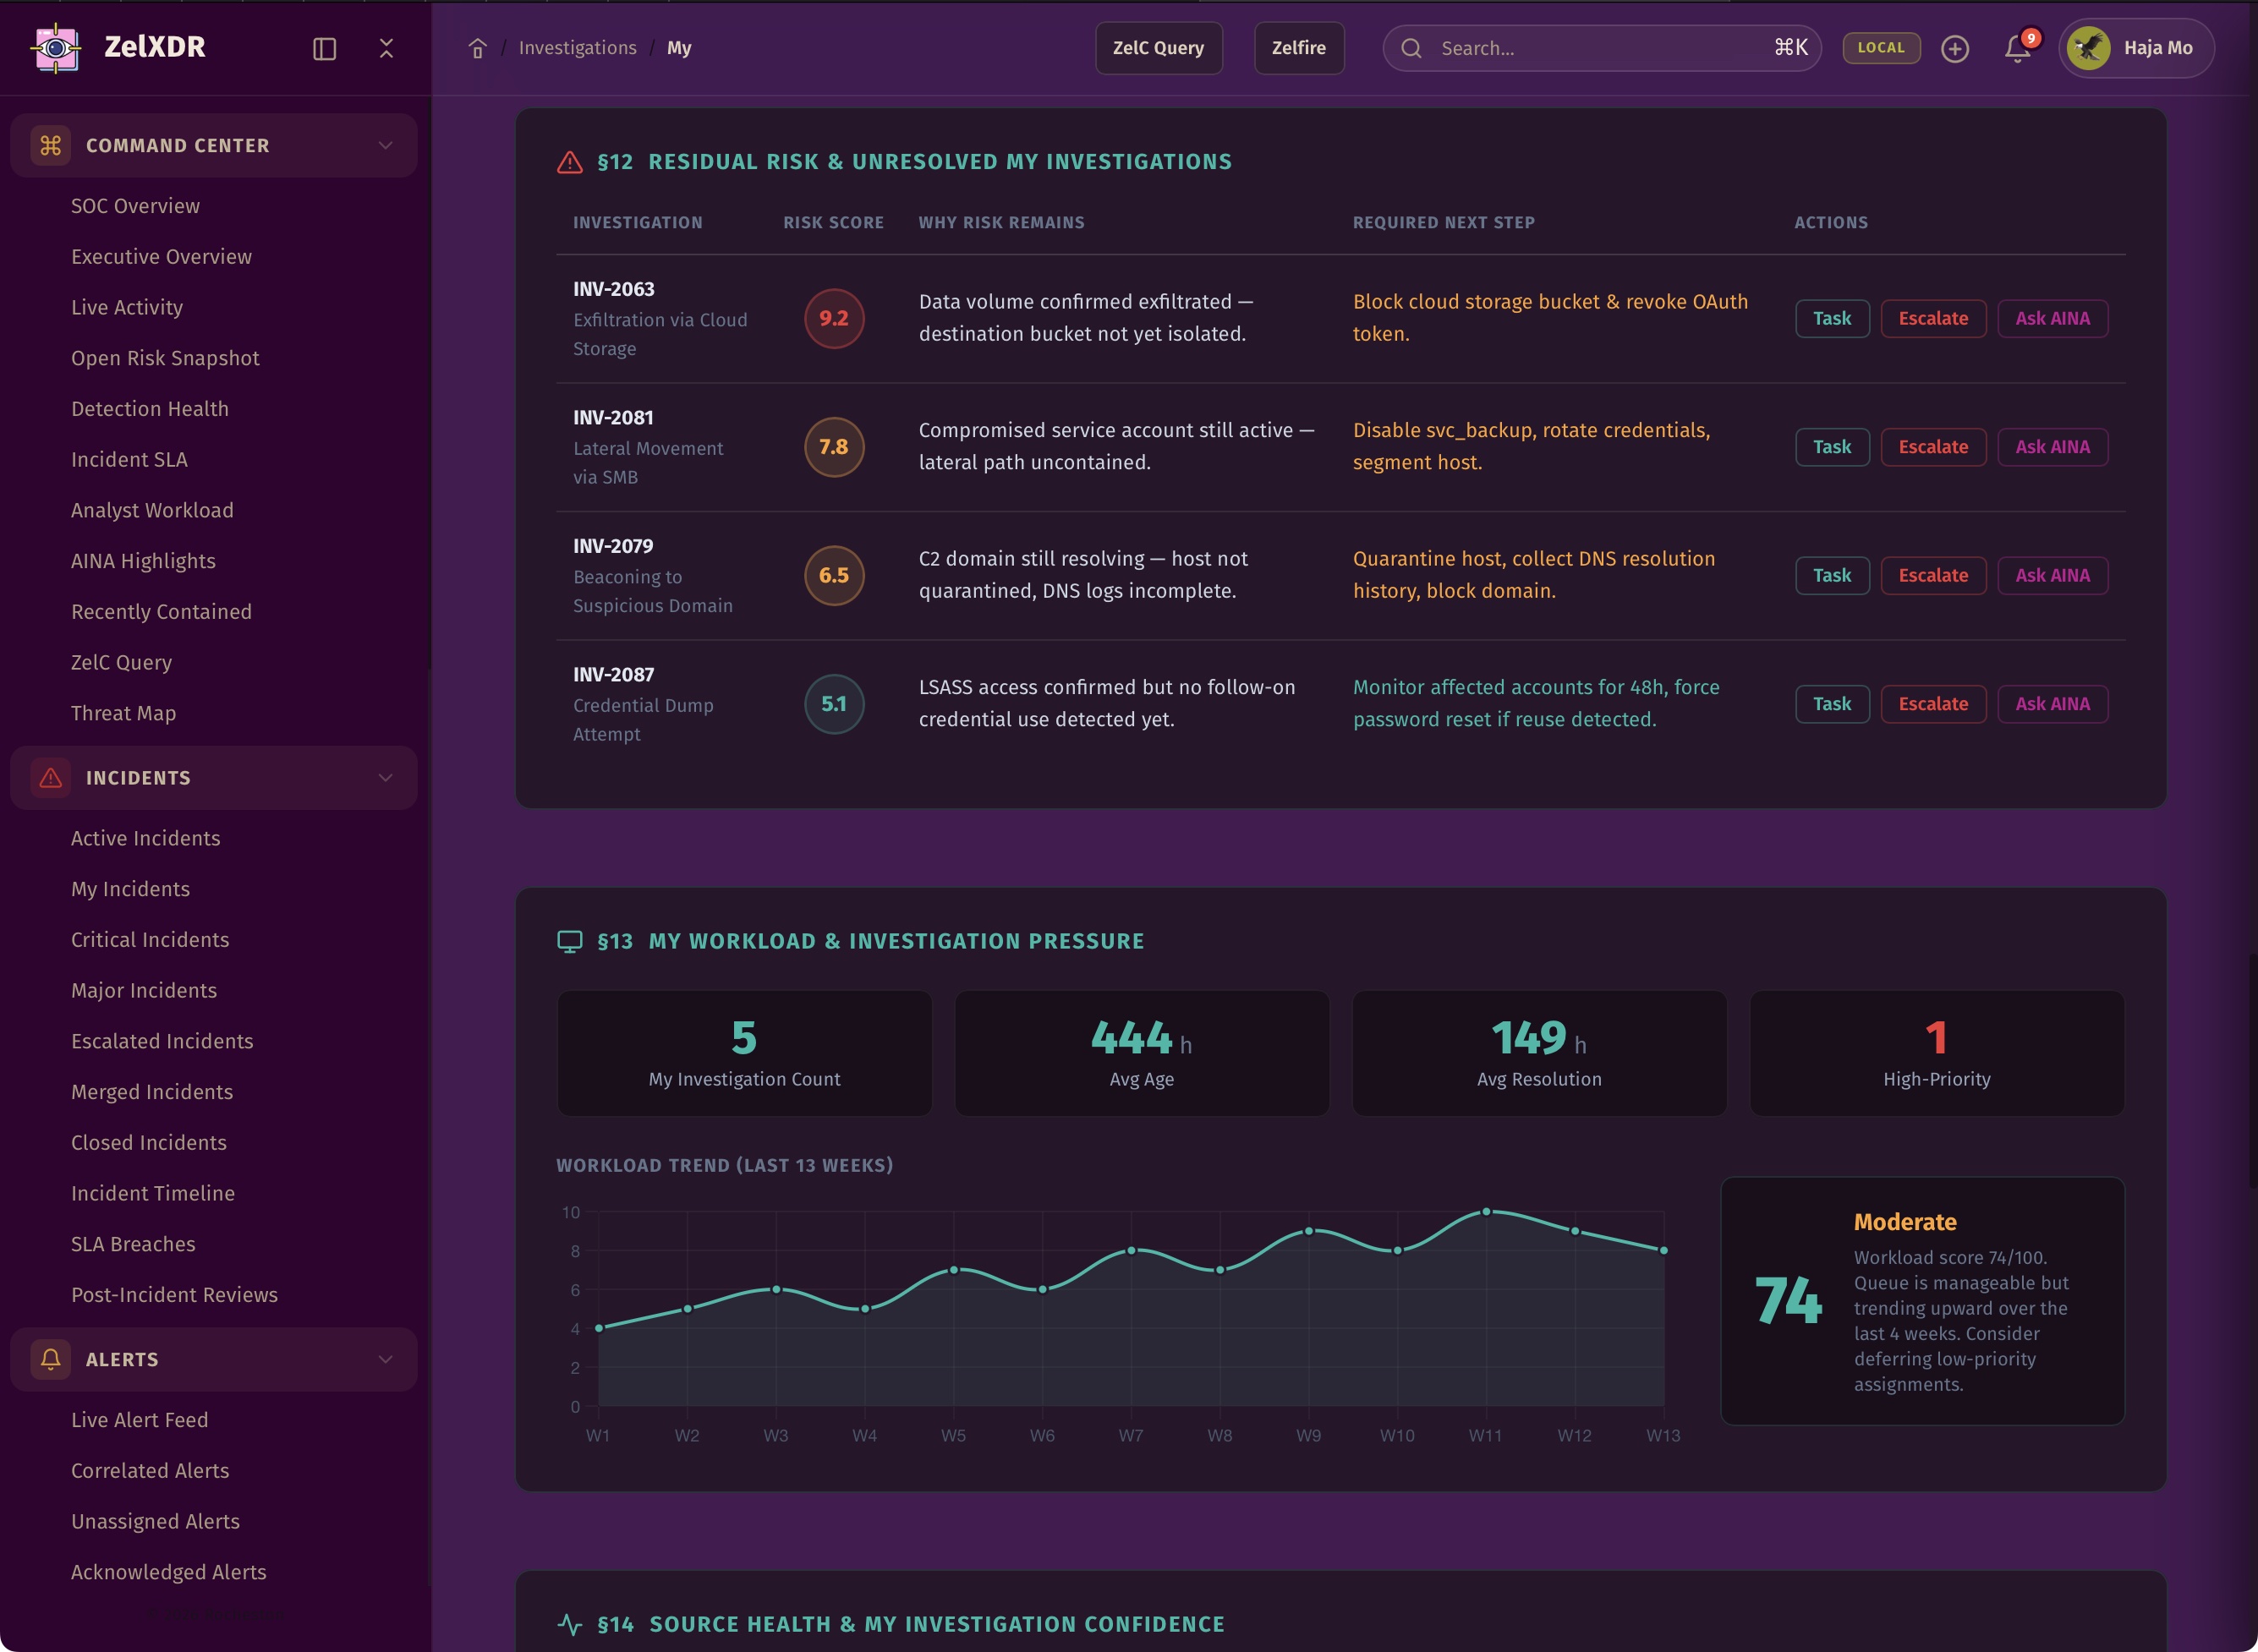
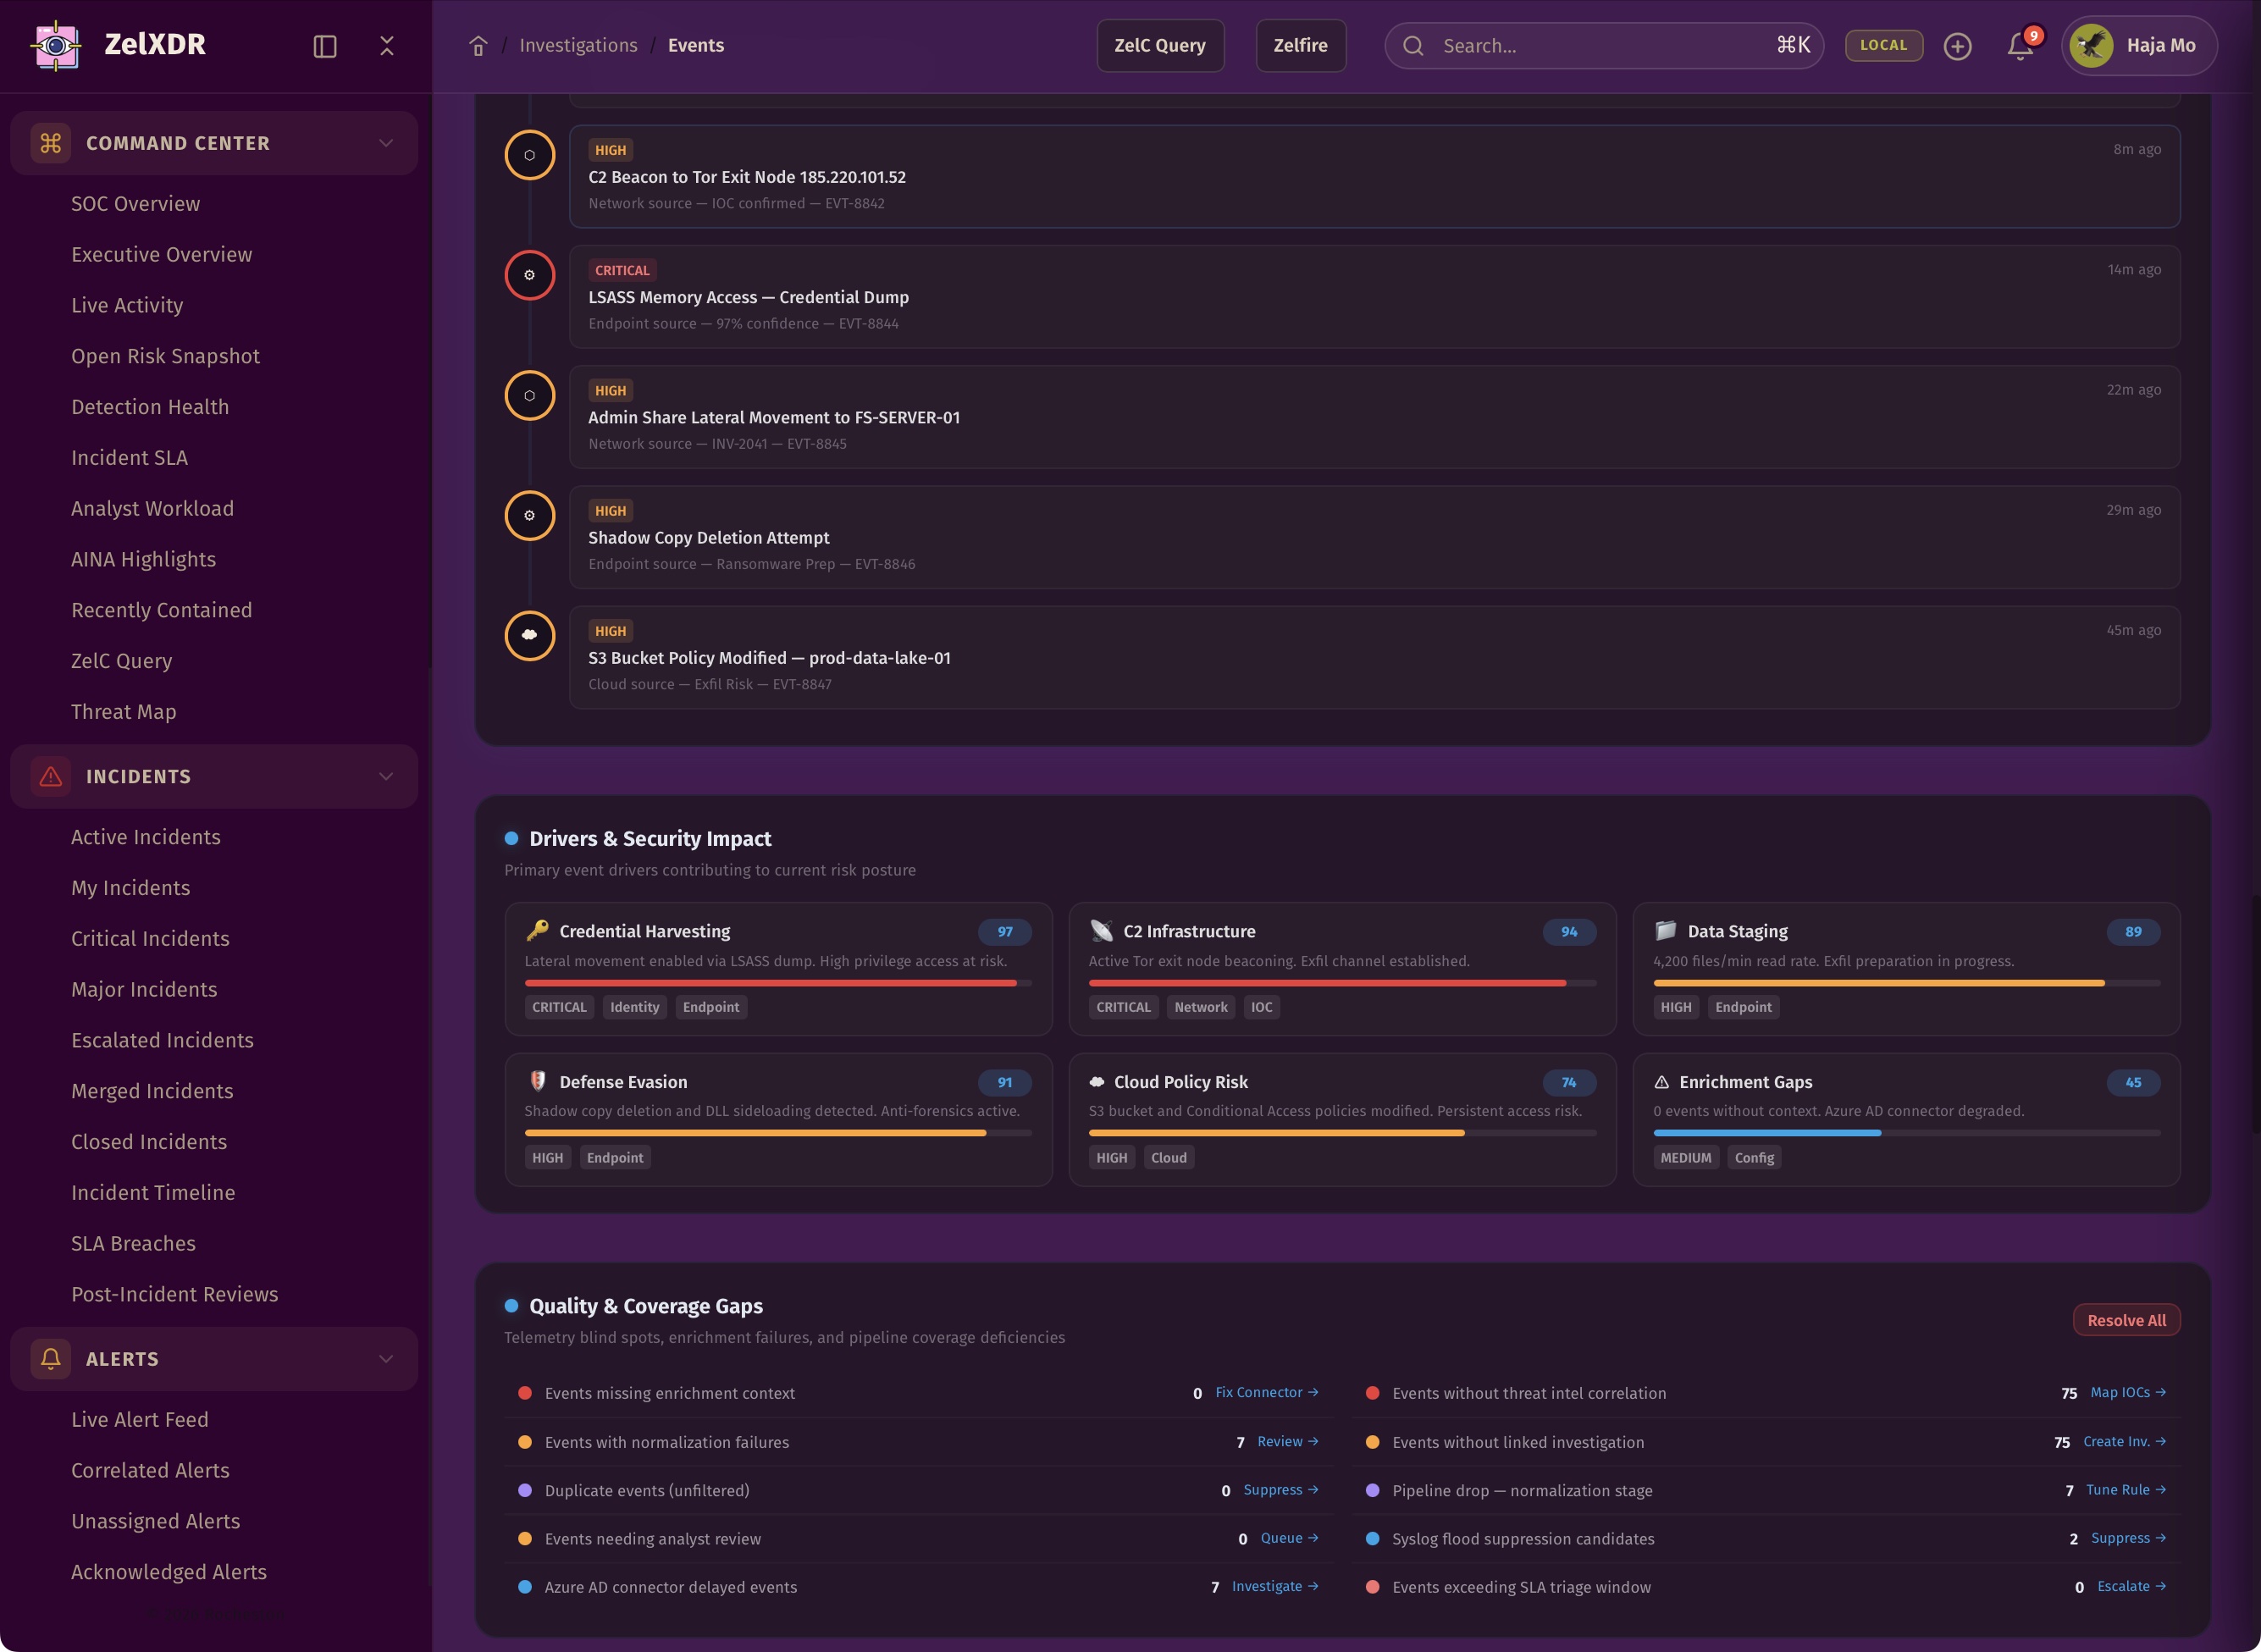
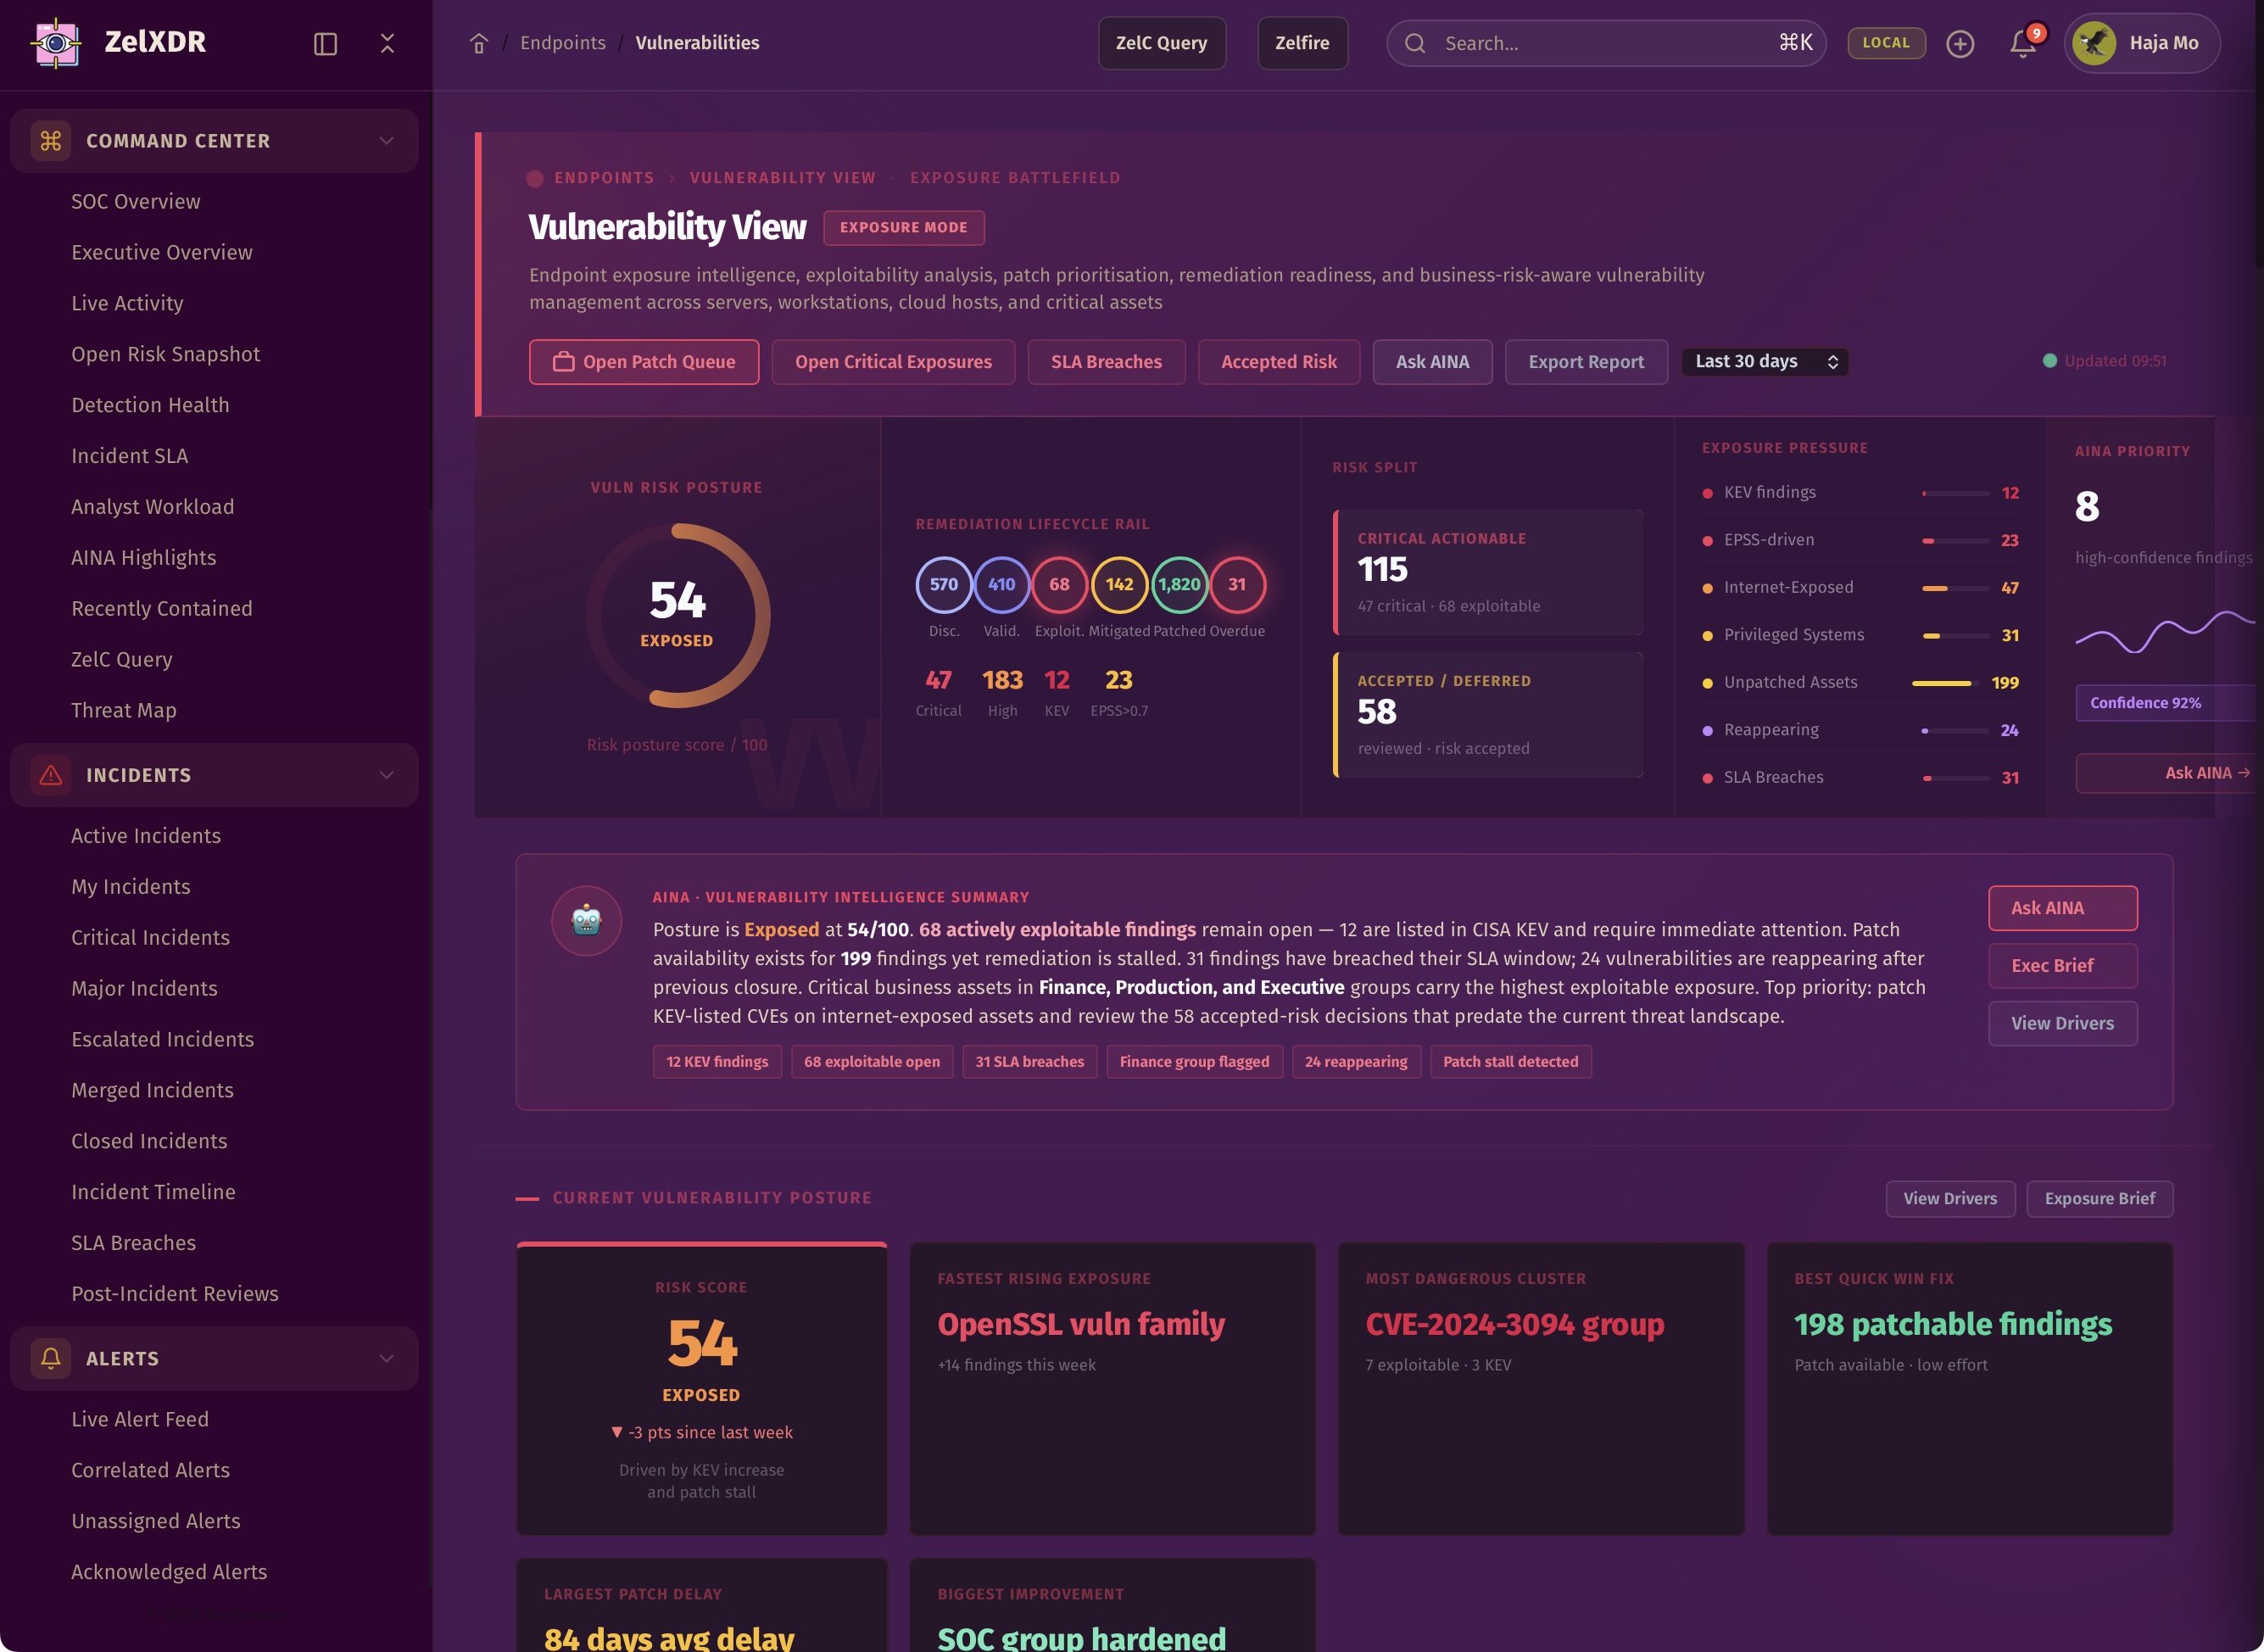
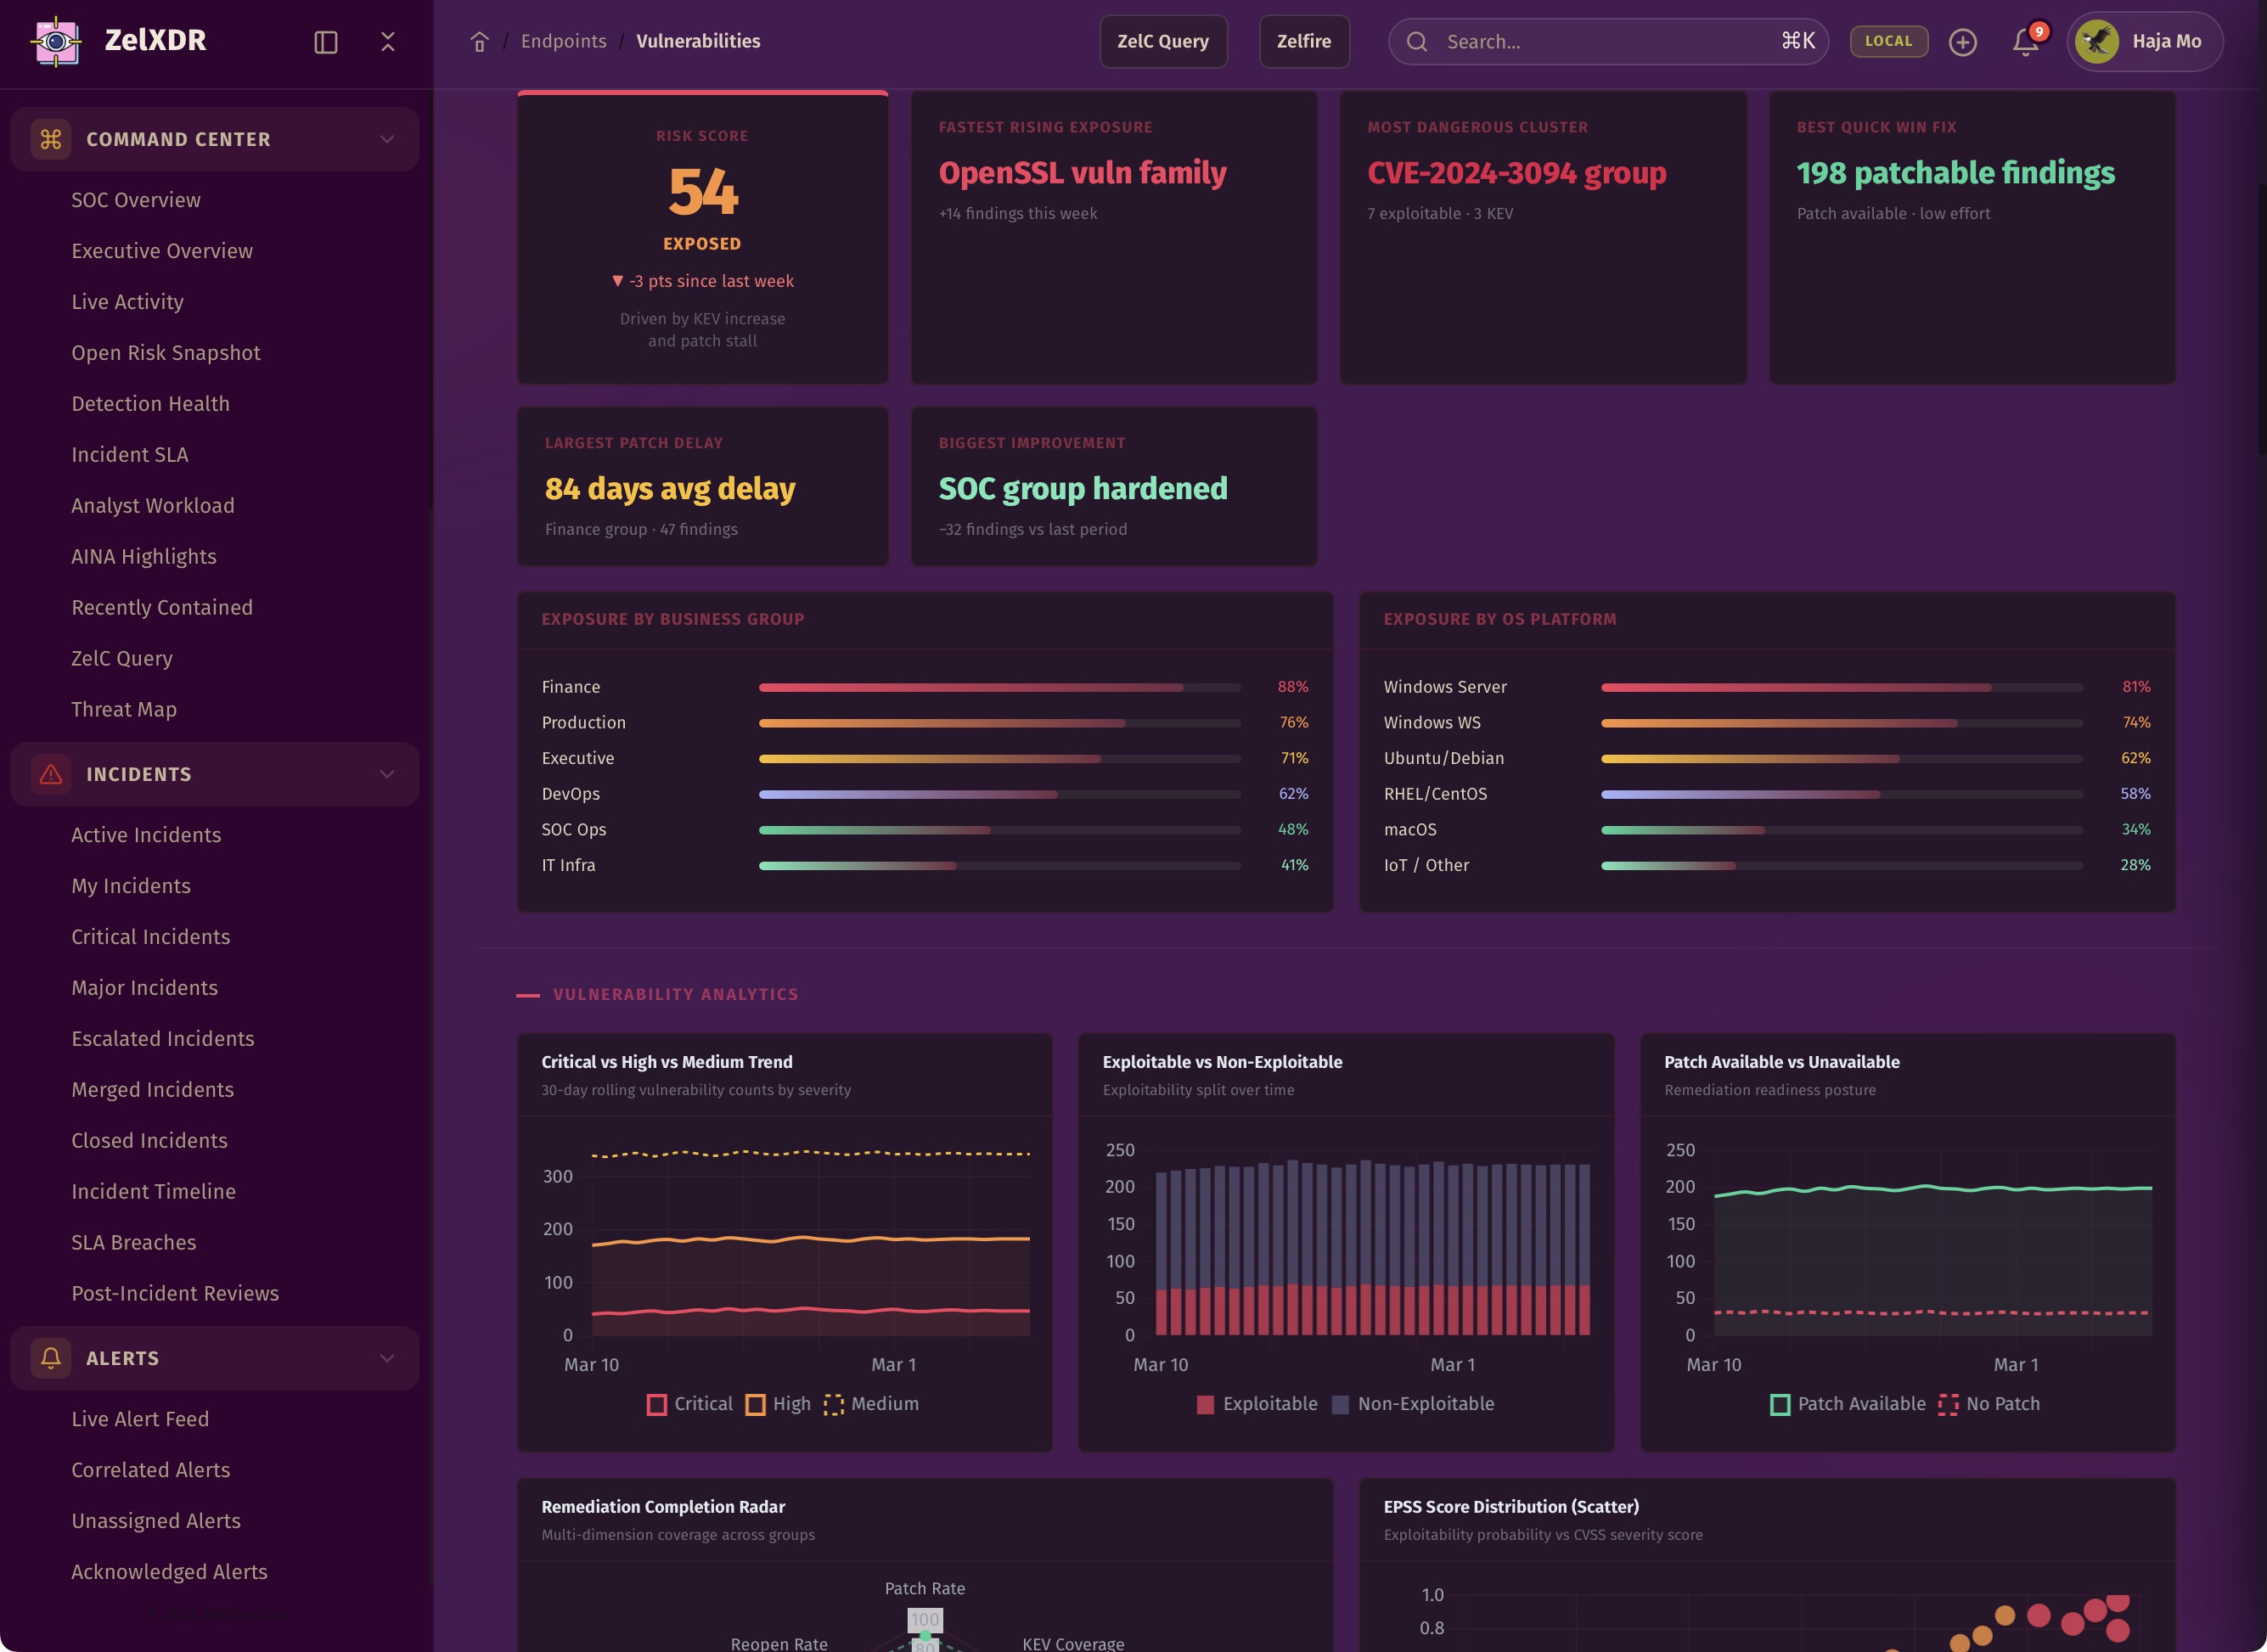
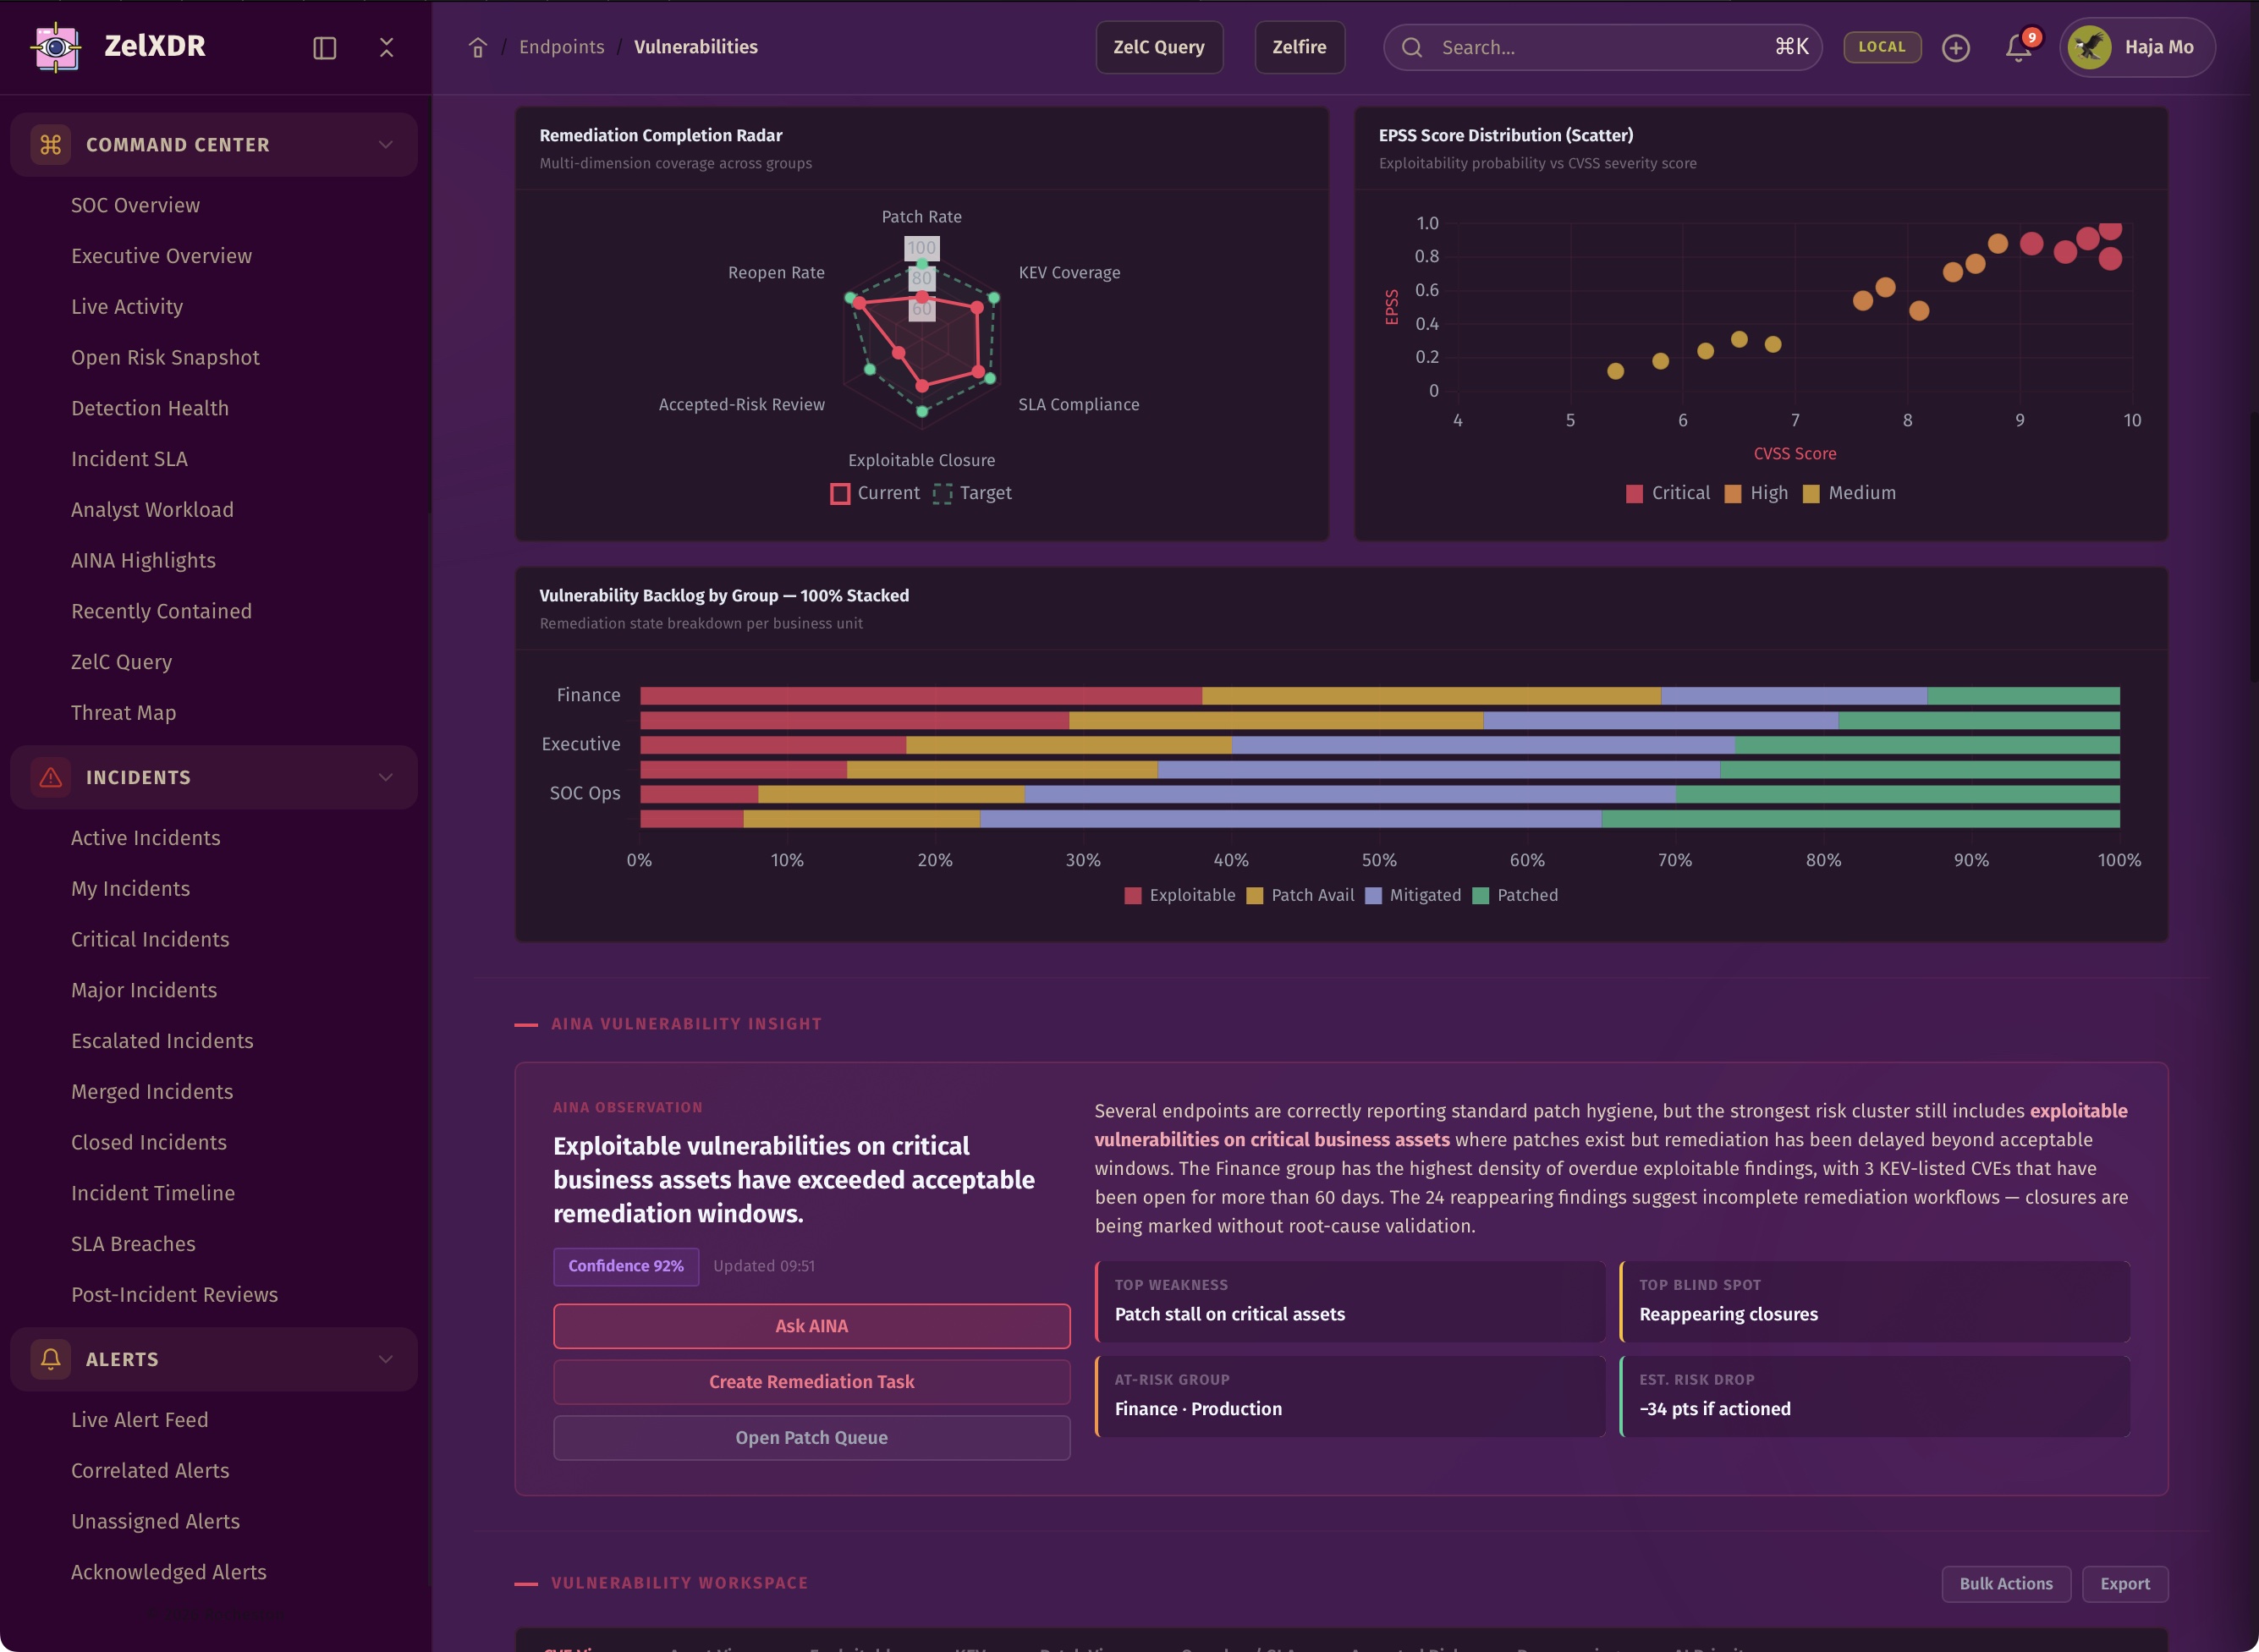
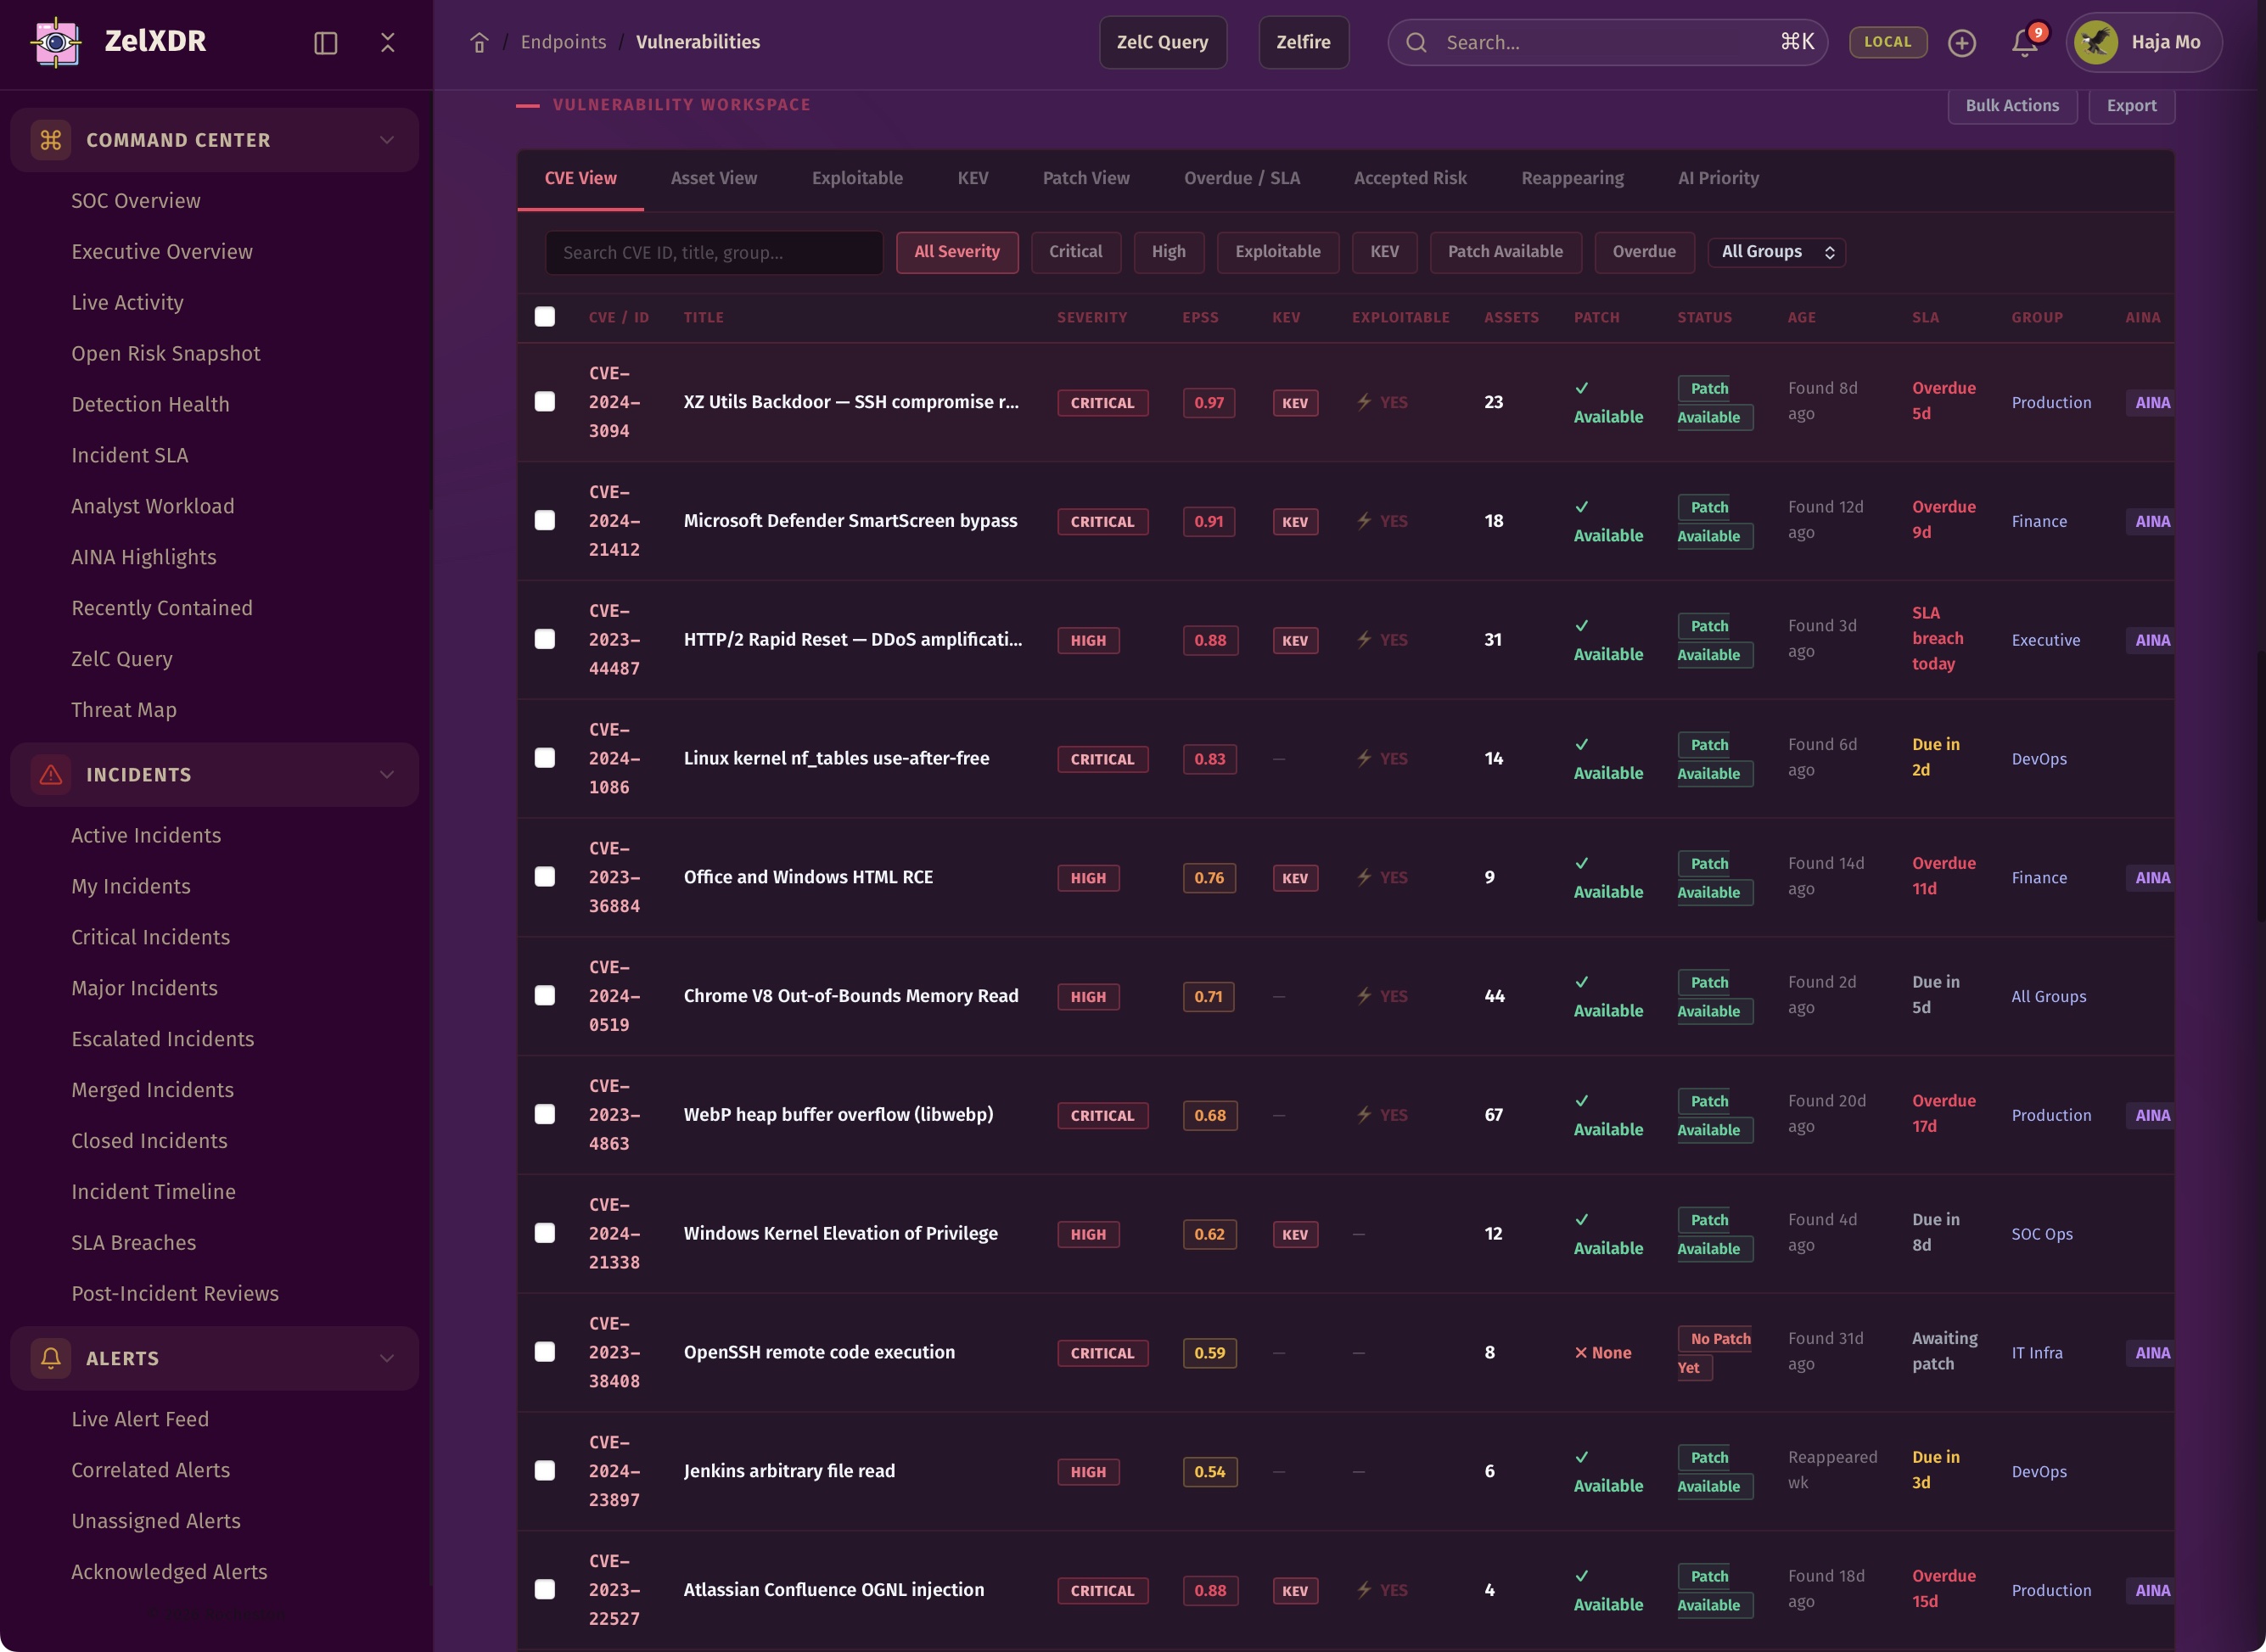
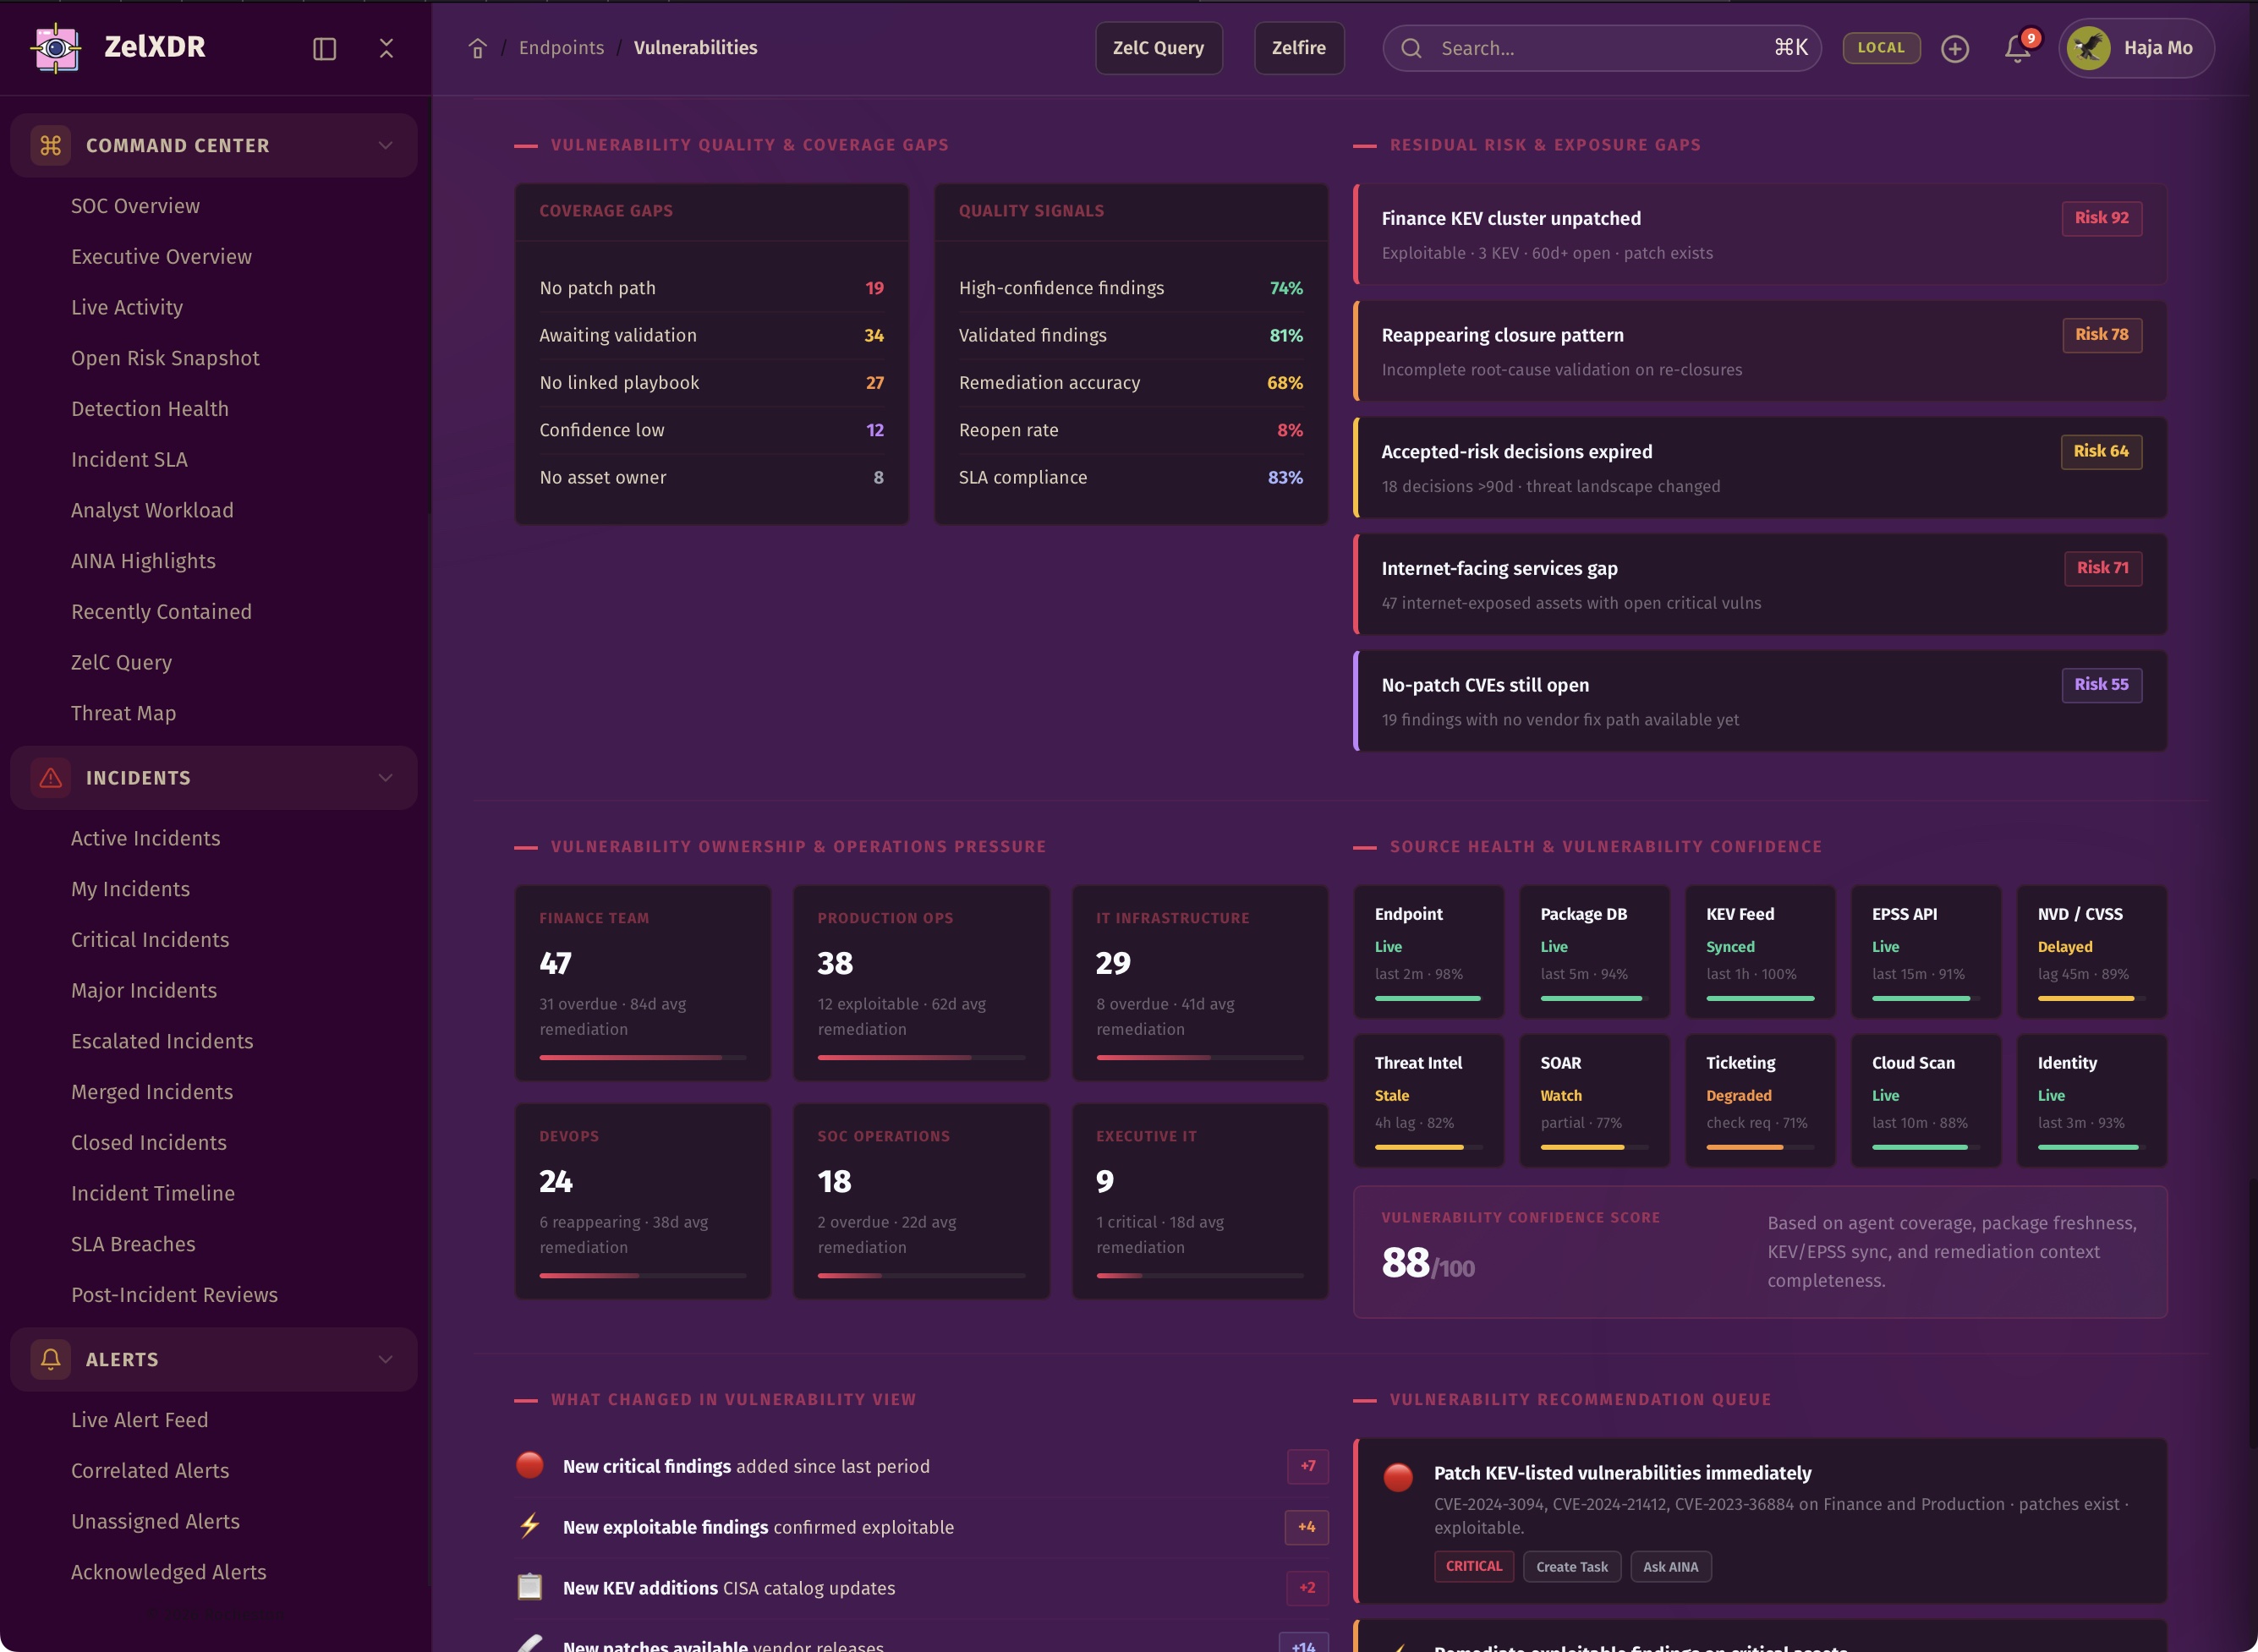
ZelXDR helps teams understand which vulnerabilities are truly urgent by combining severity, exploitability, asset criticality, business impact, and remediation readiness into one operational view.
Not every vulnerability is equal. Prioritization is defense.
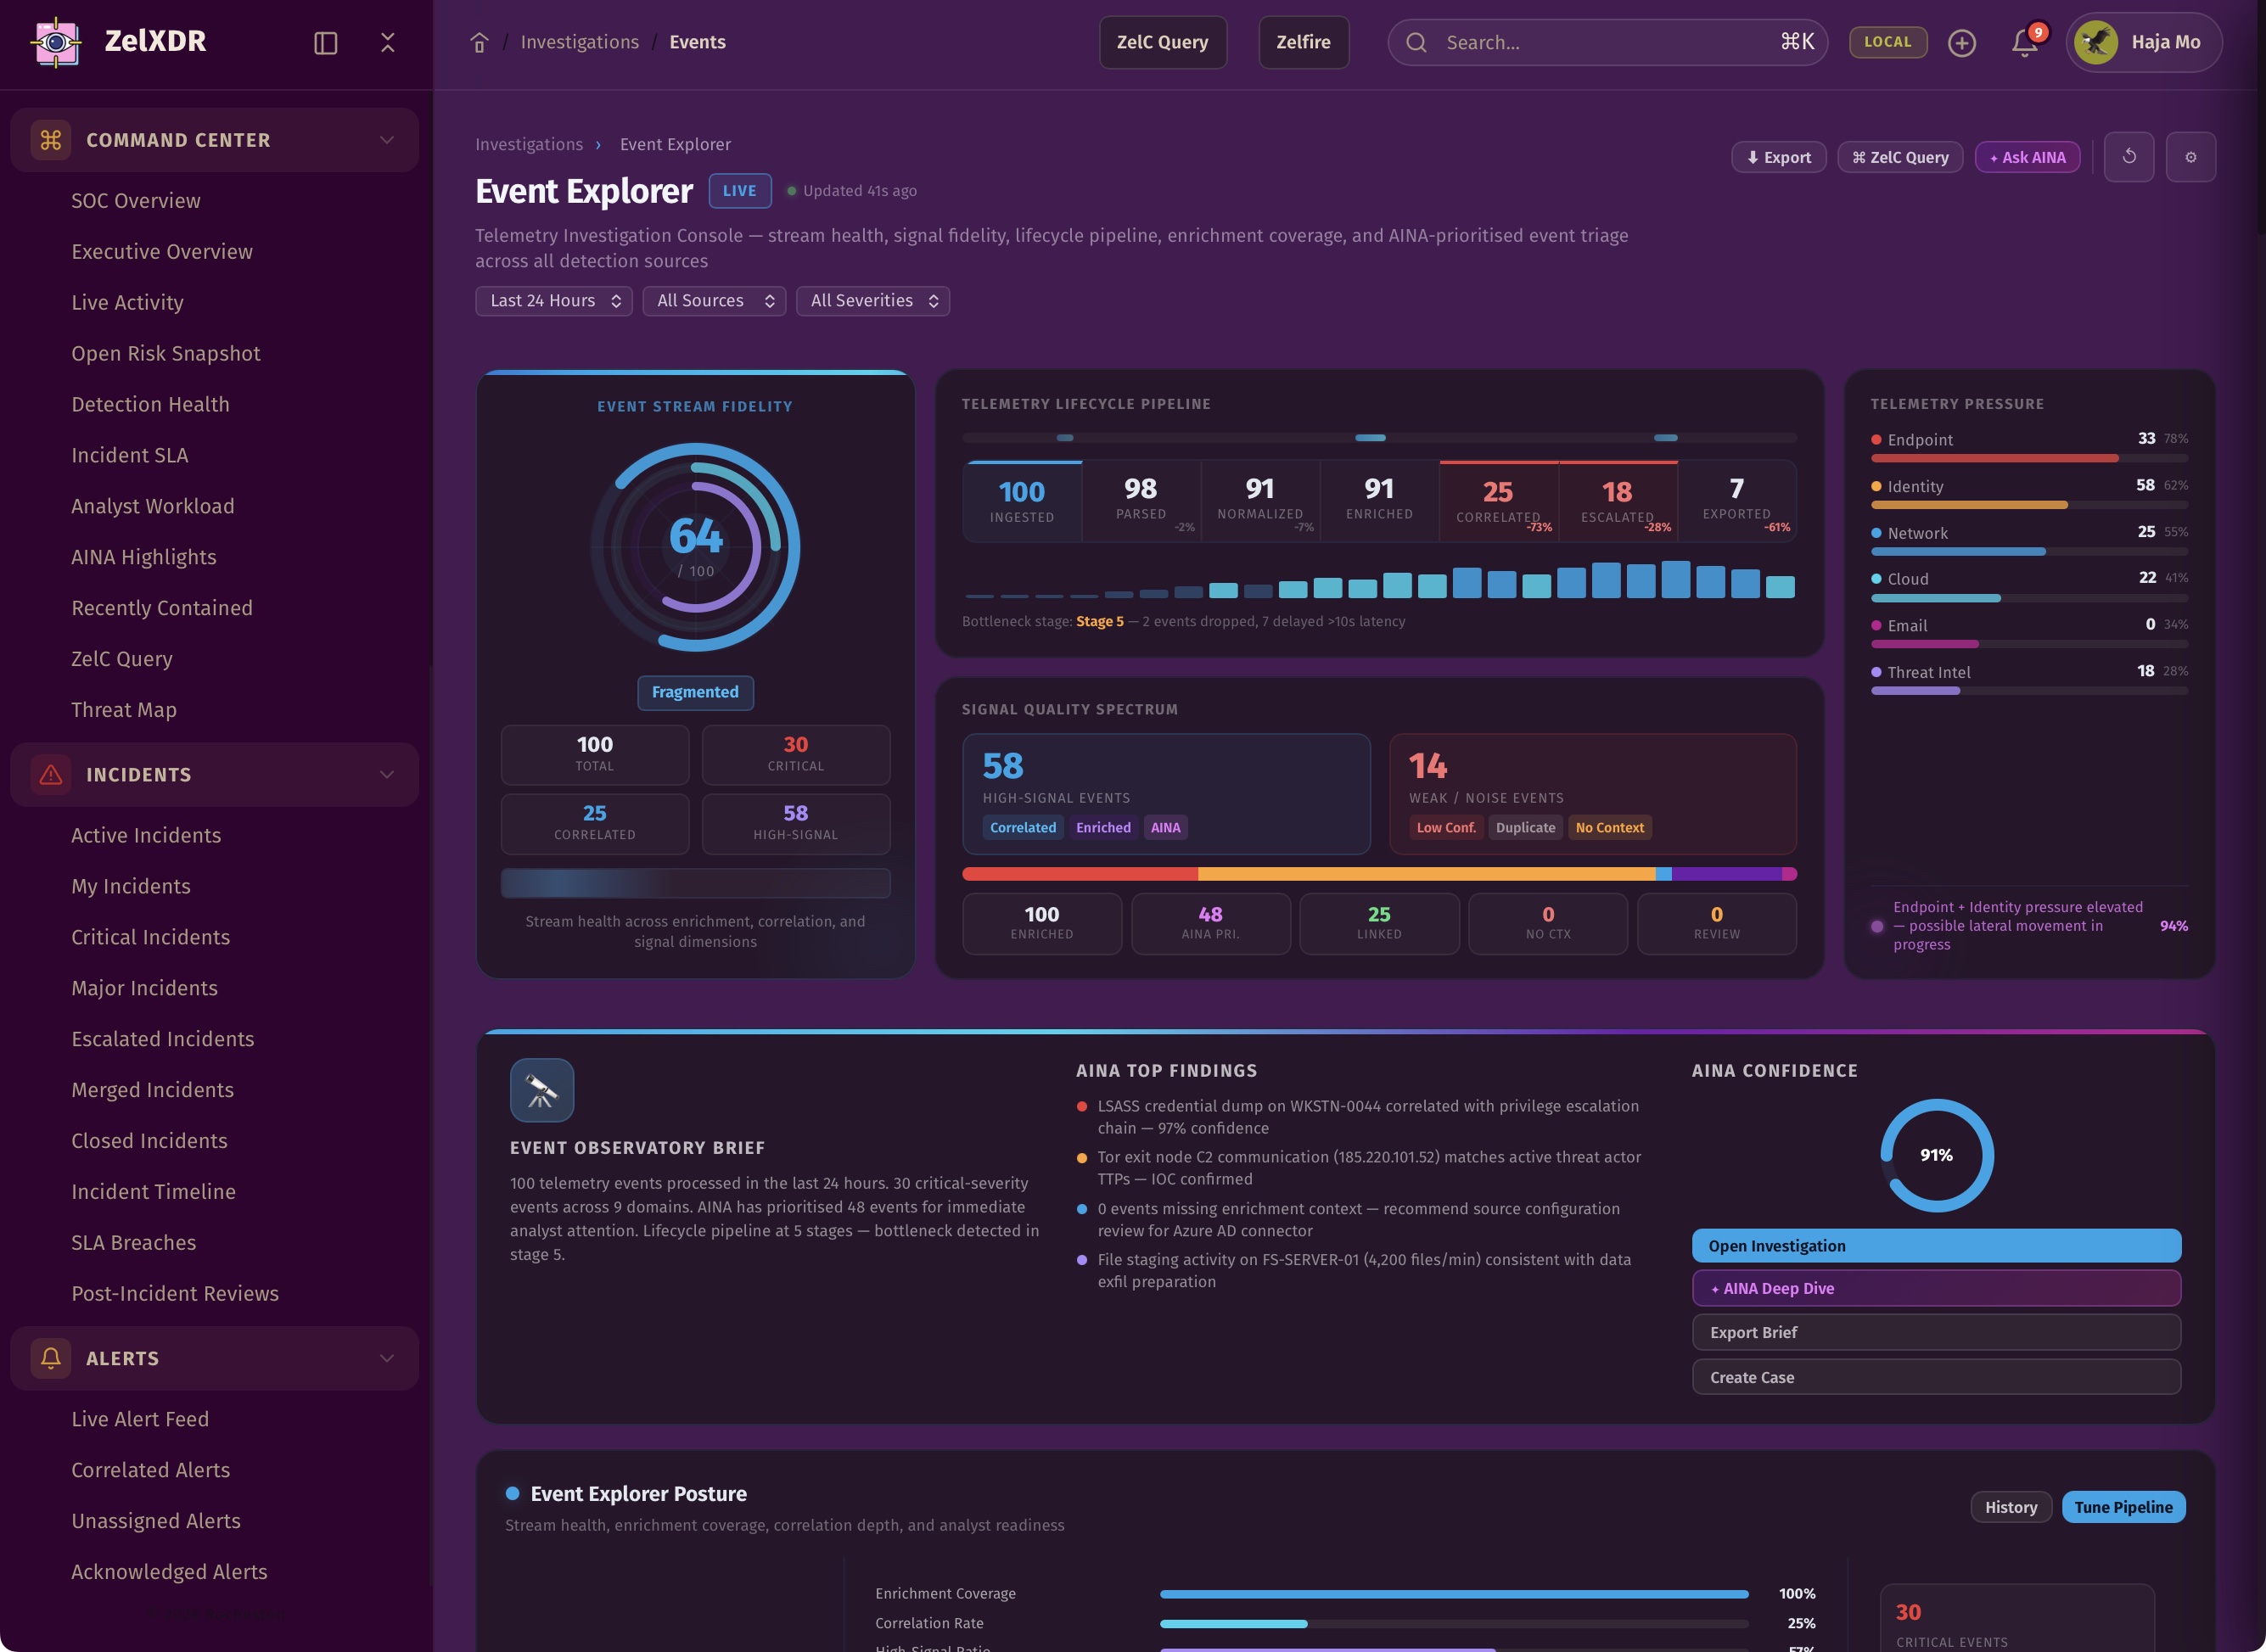
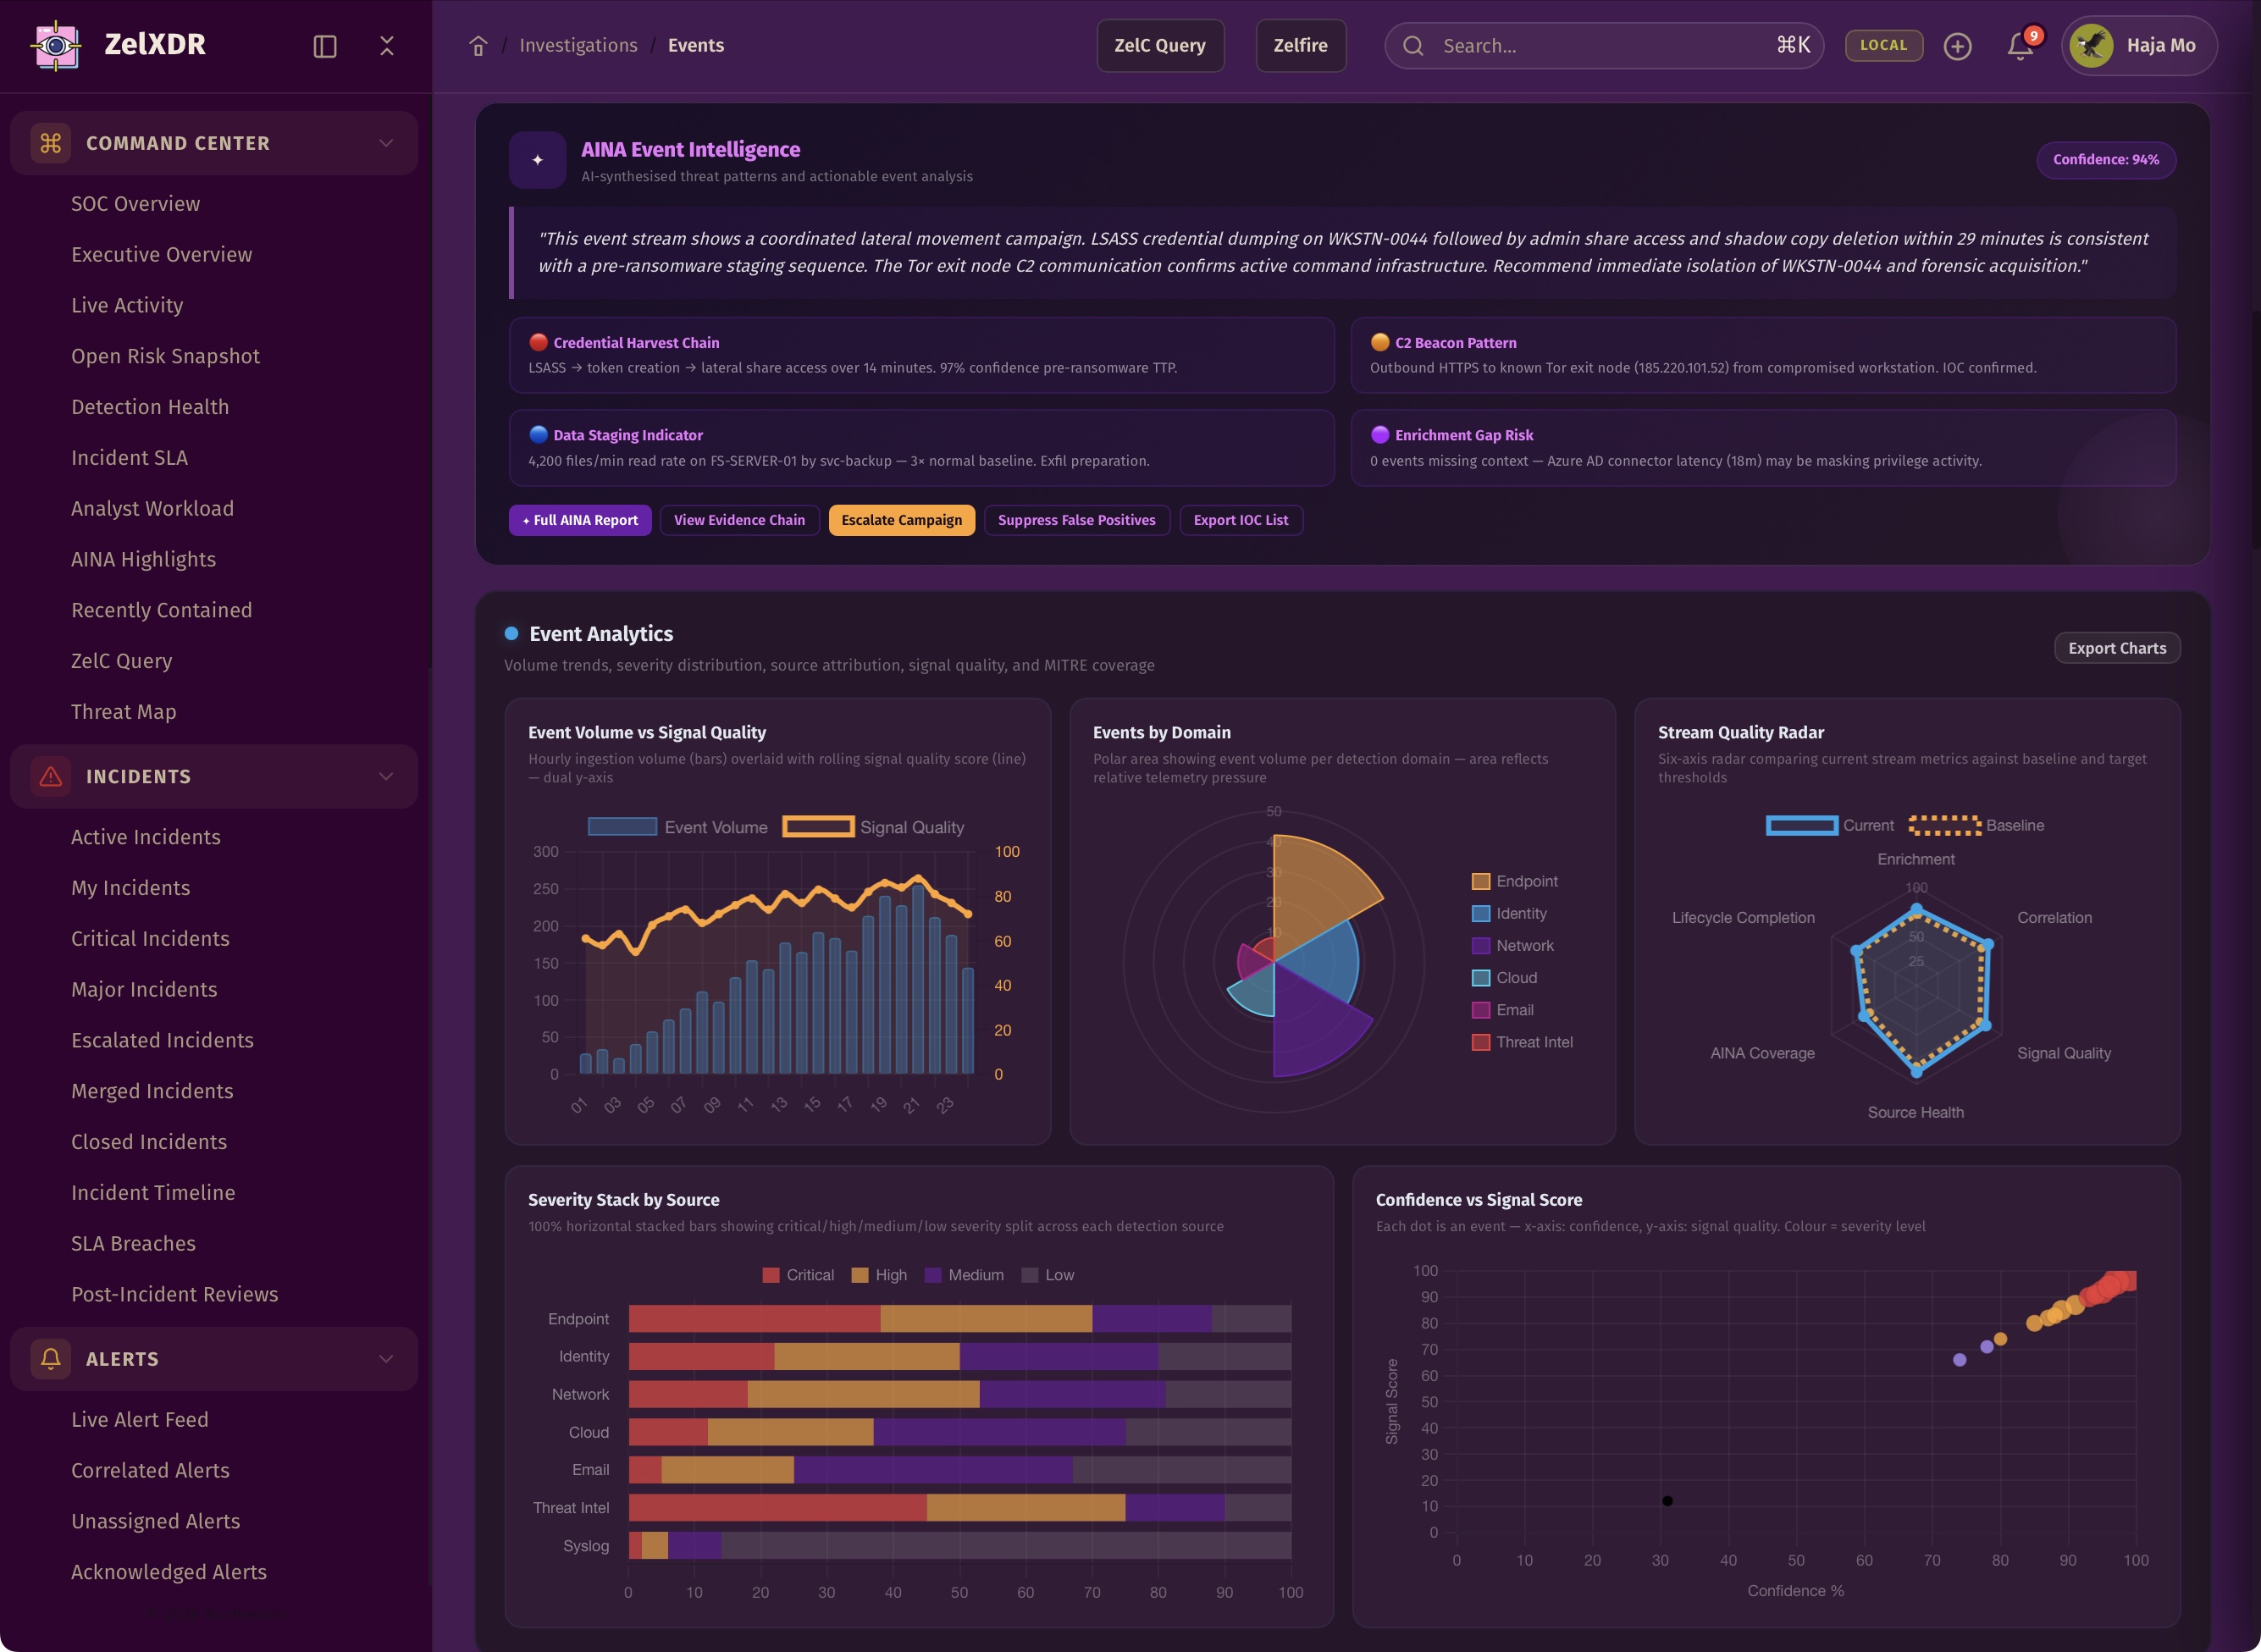
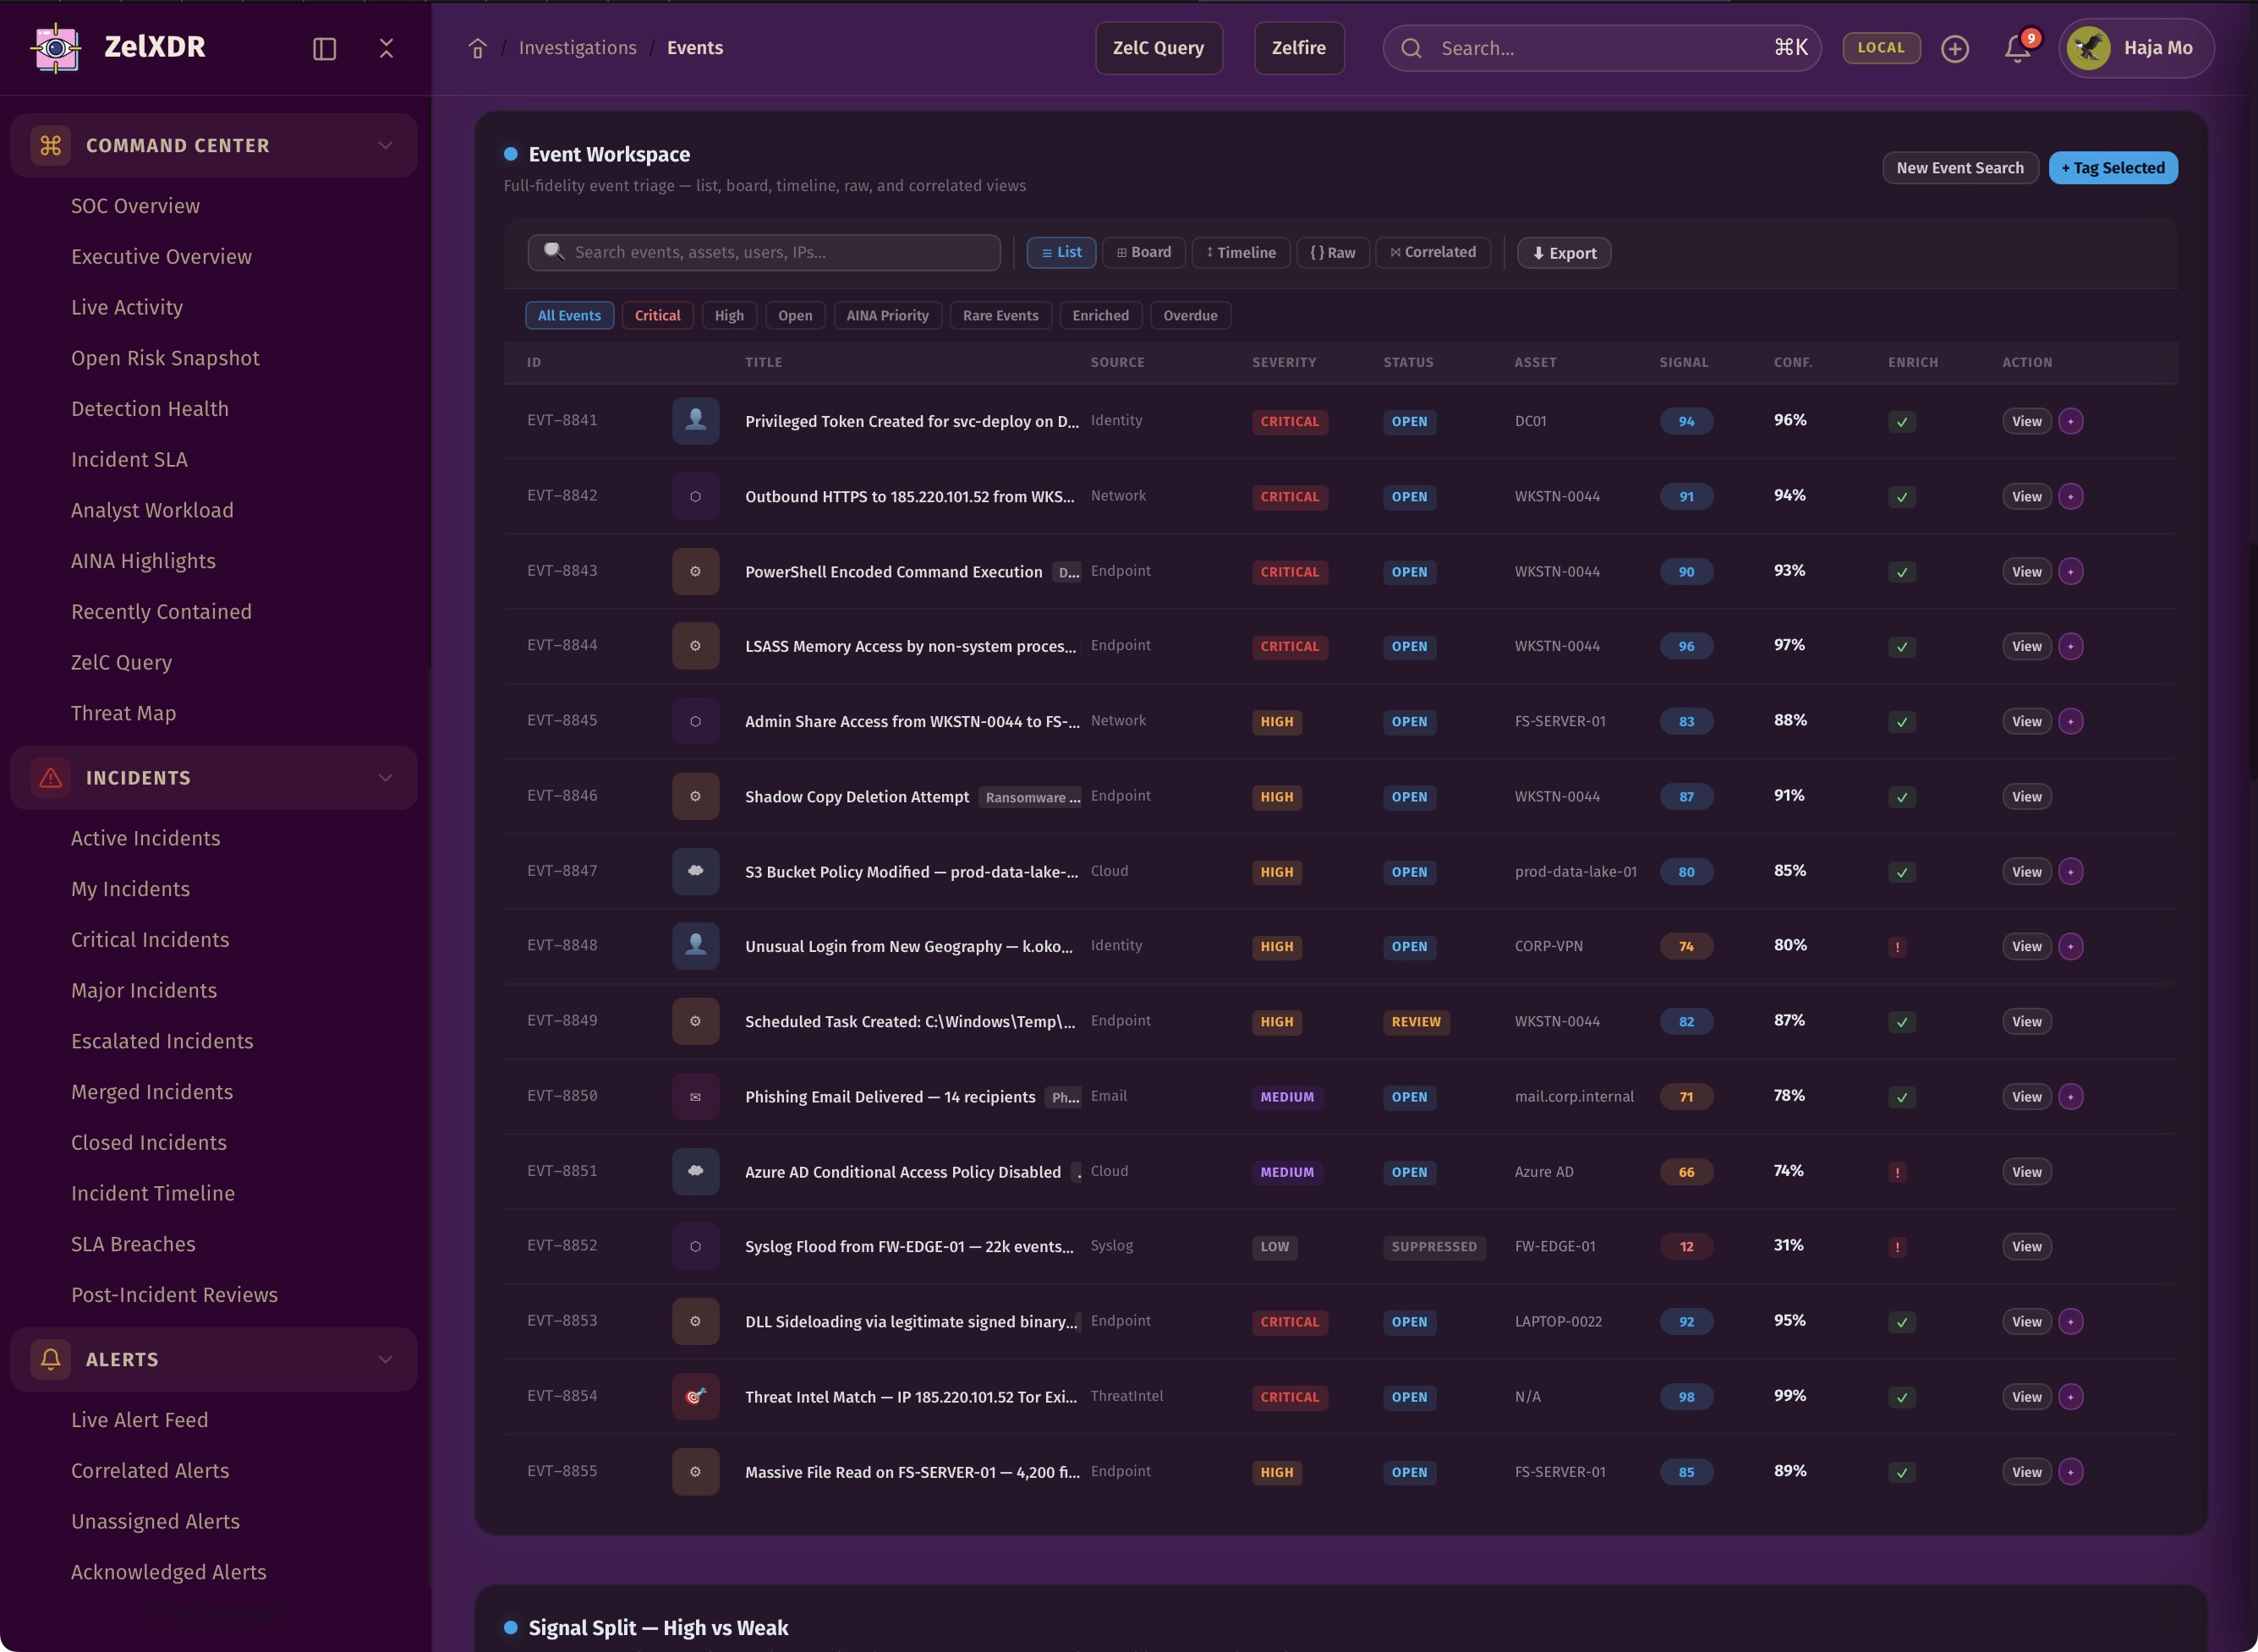
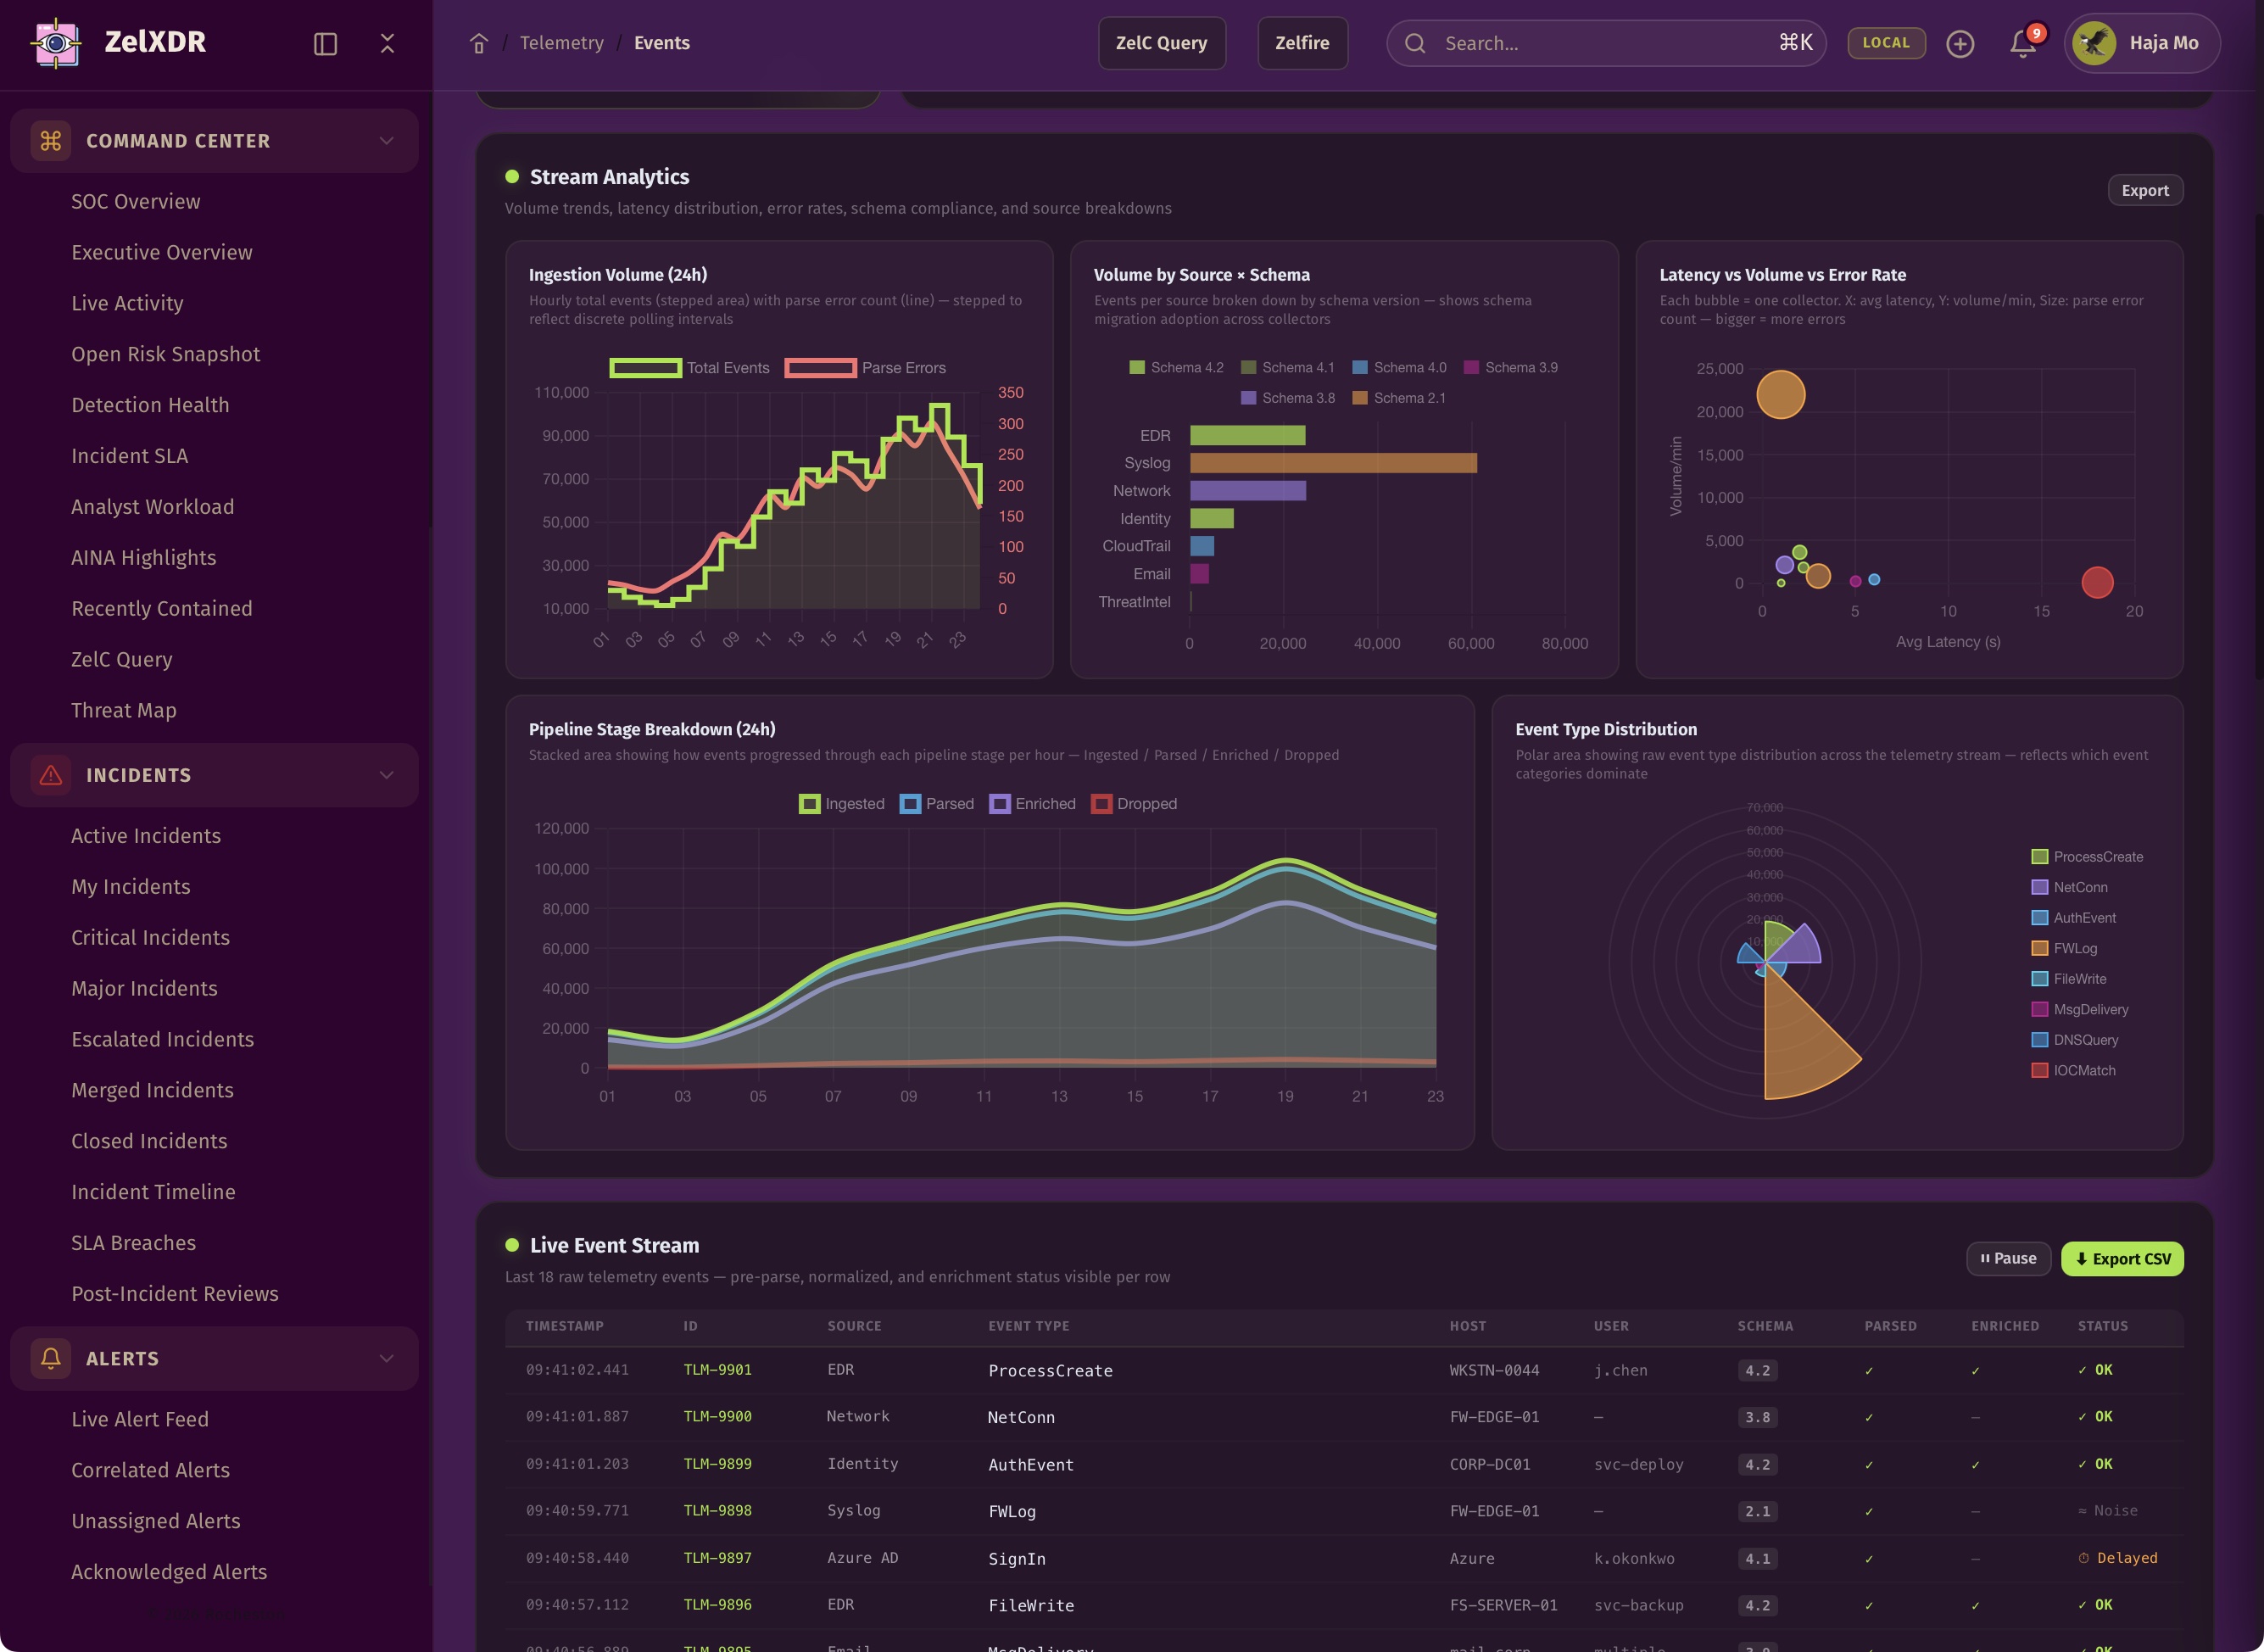
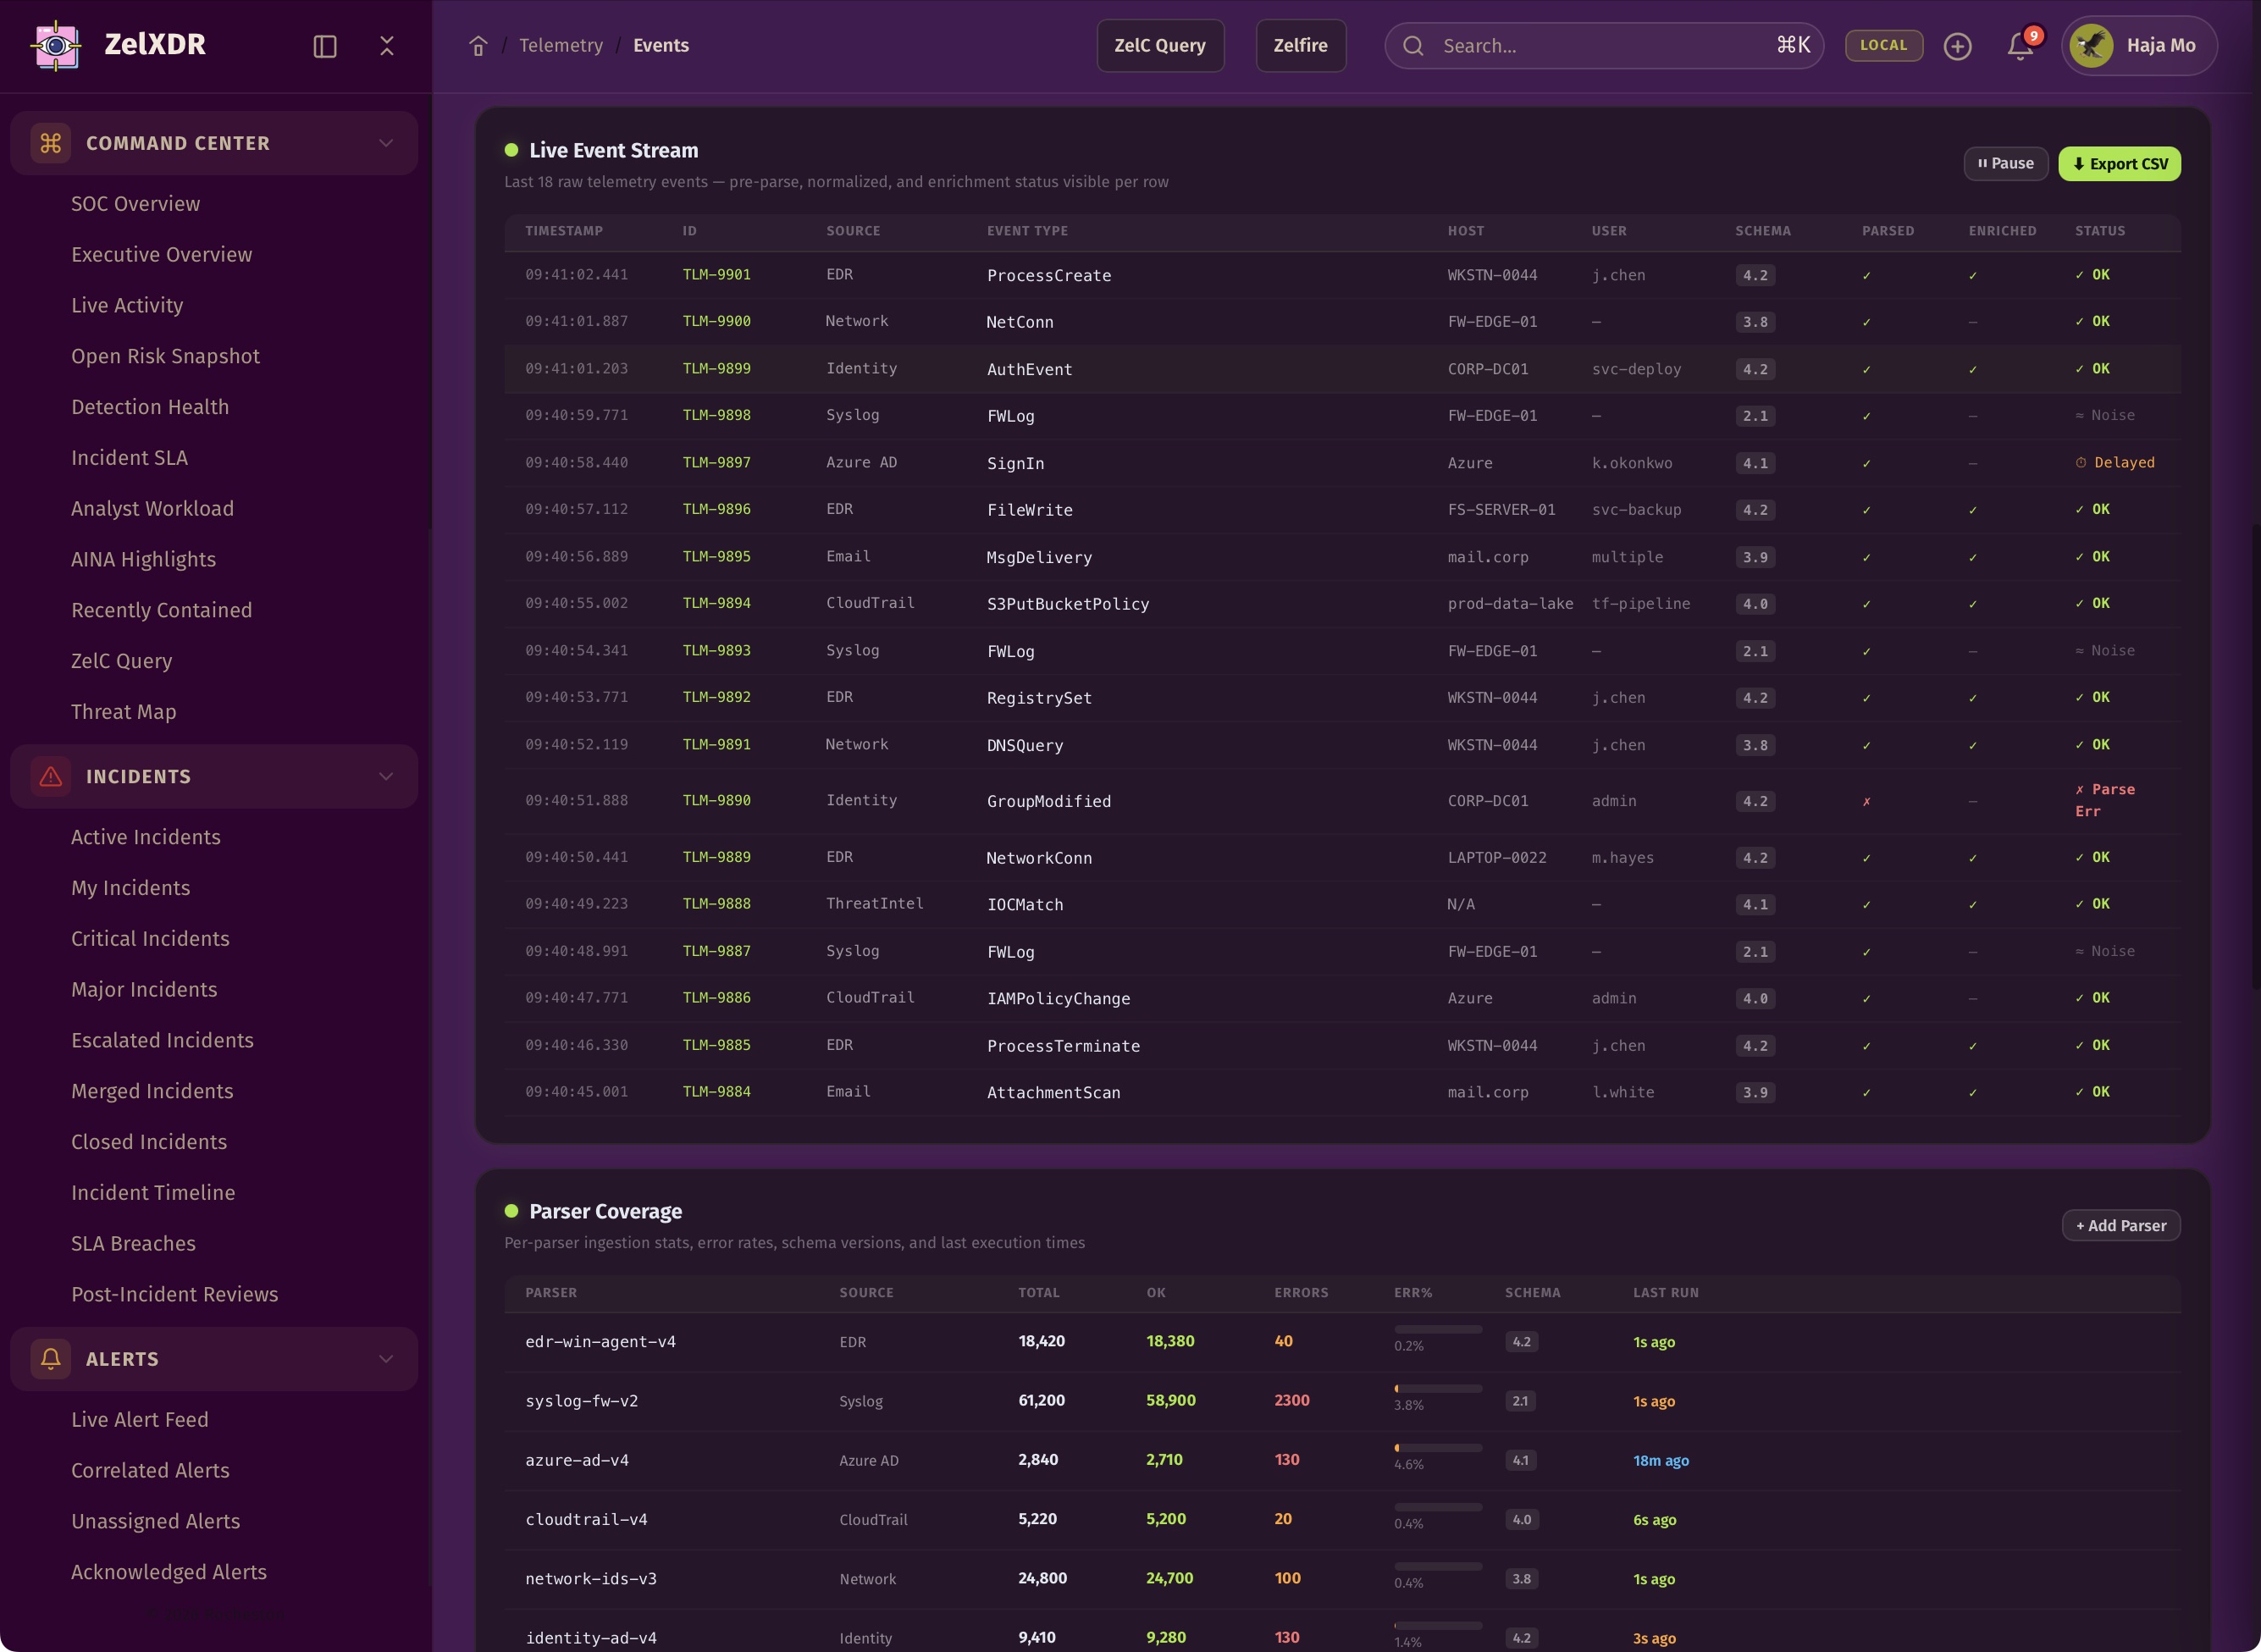
The Event Explorer lets teams search, pivot, filter, and investigate live and historical telemetry across identities, endpoints, cloud, network, and email. It turns event streams into actionable insight.
Events are noise until context makes them intelligence.
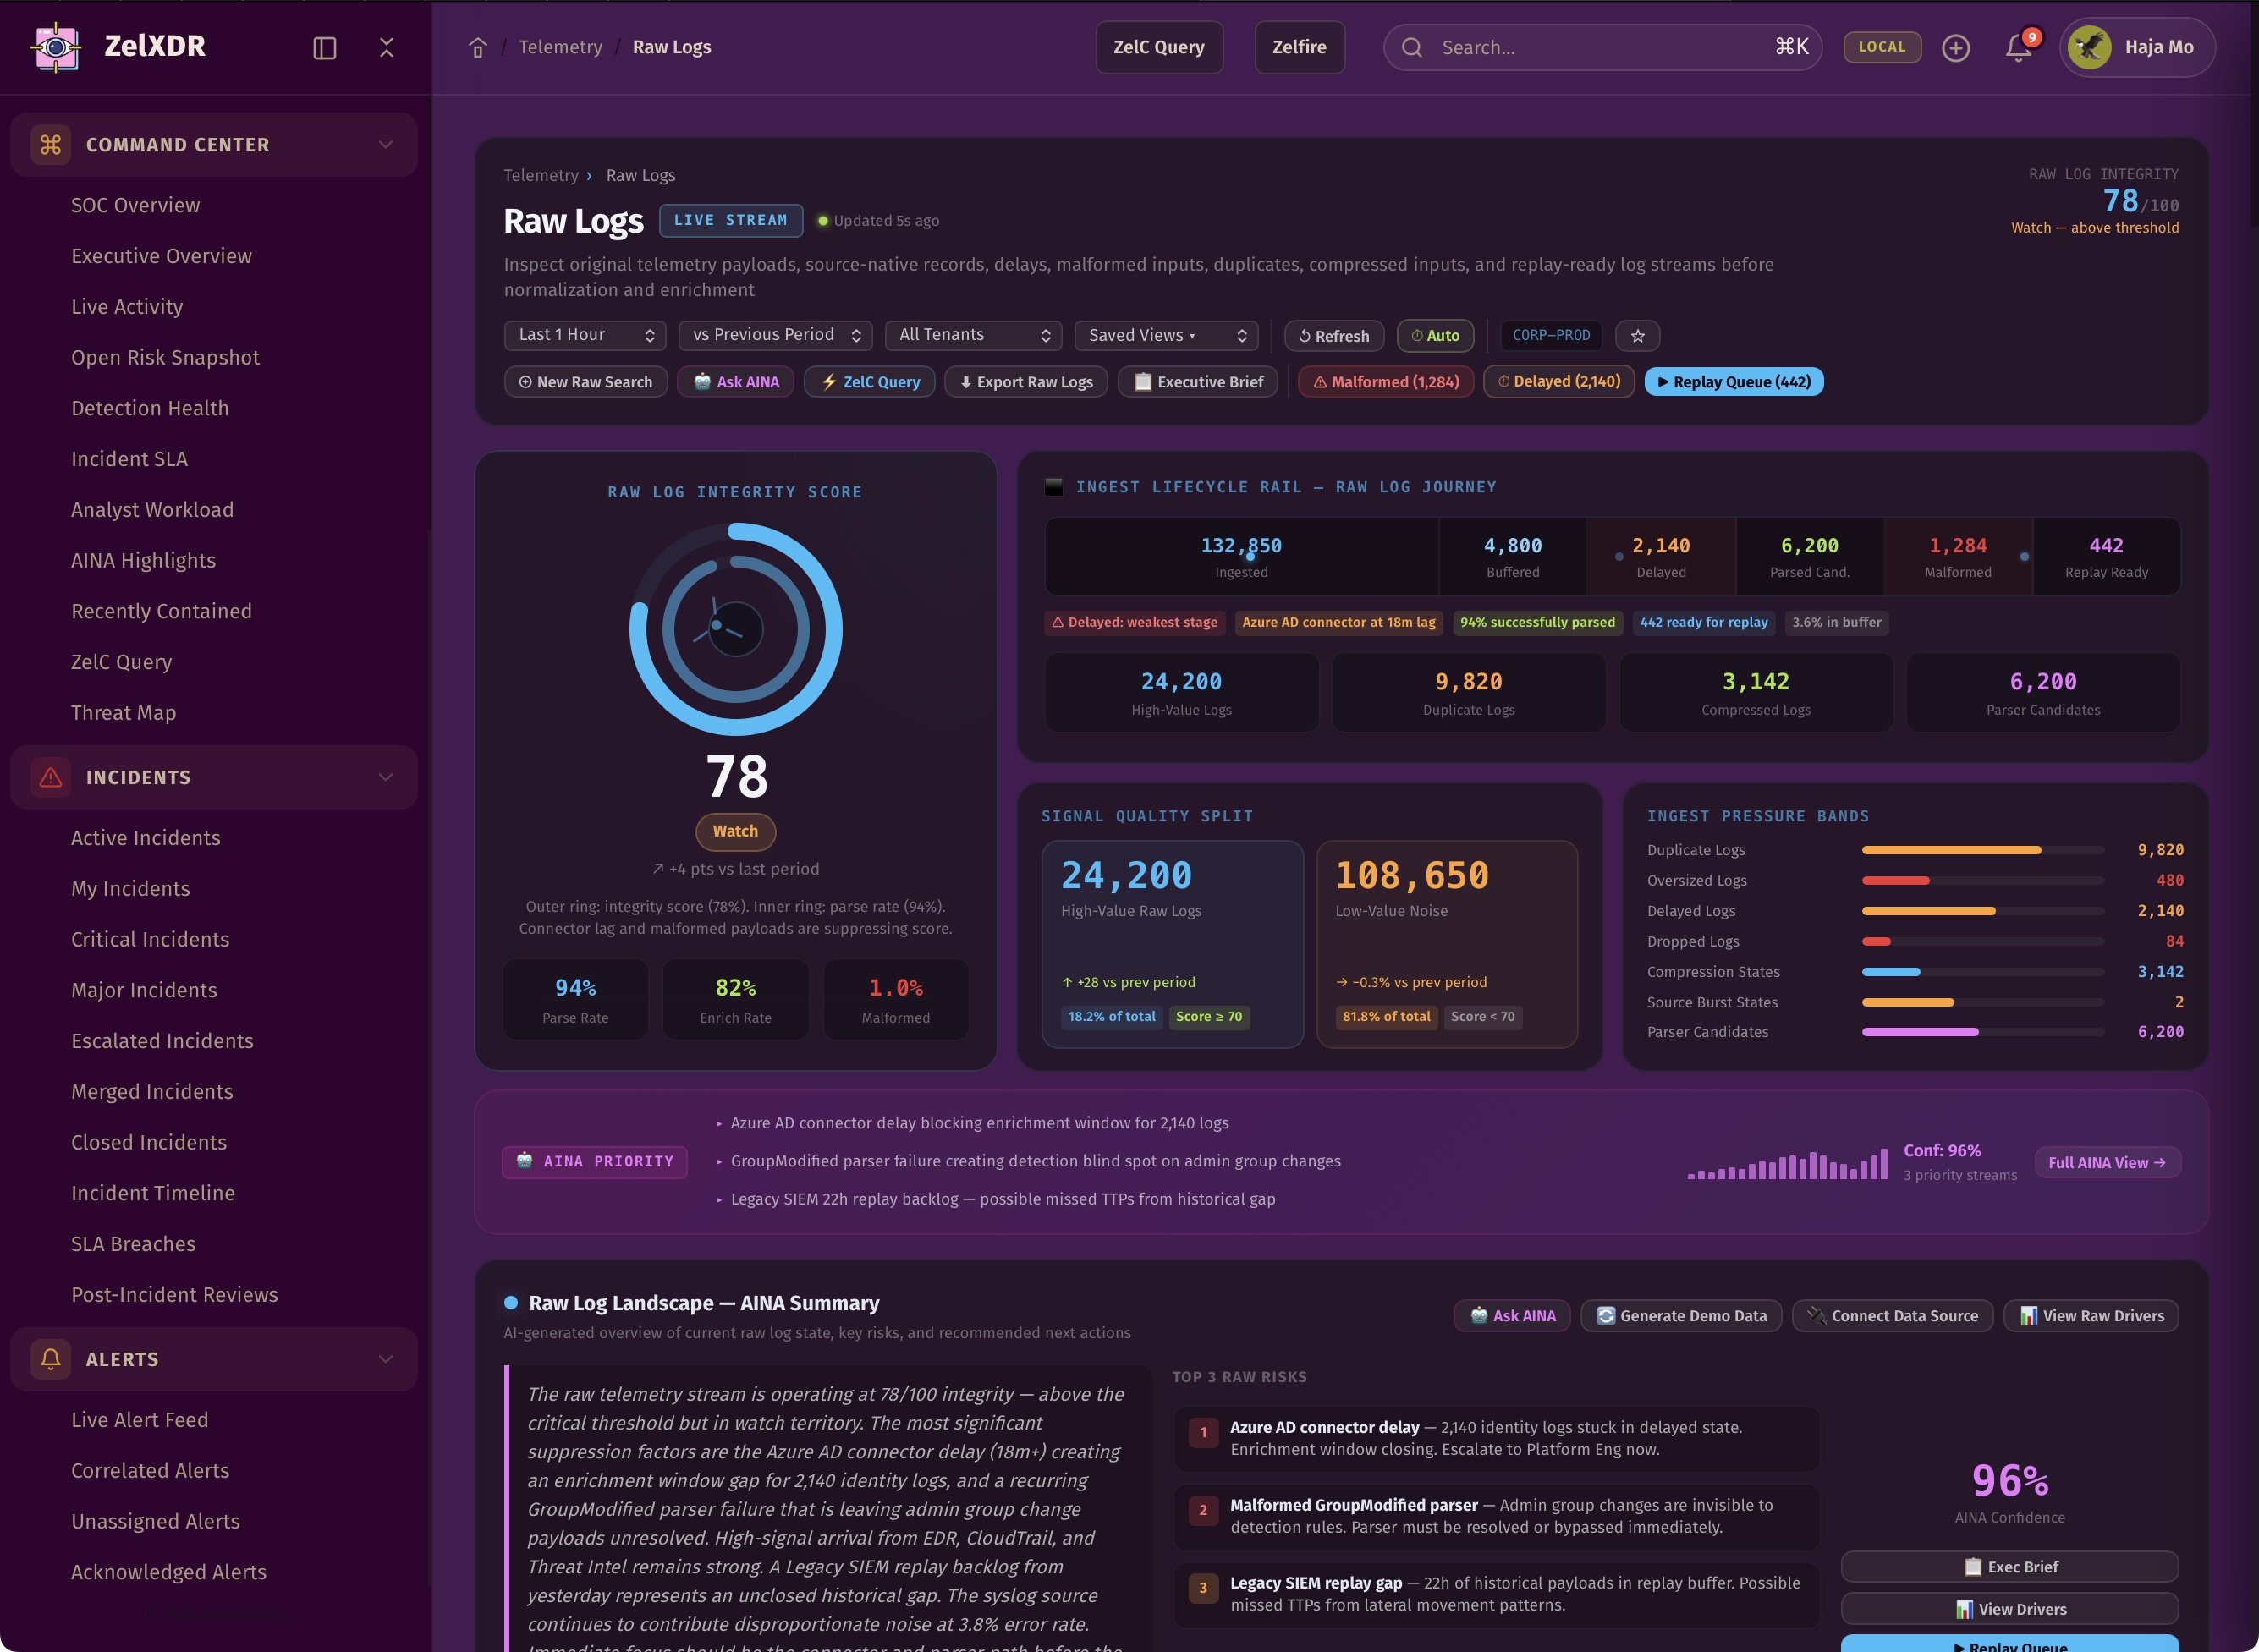
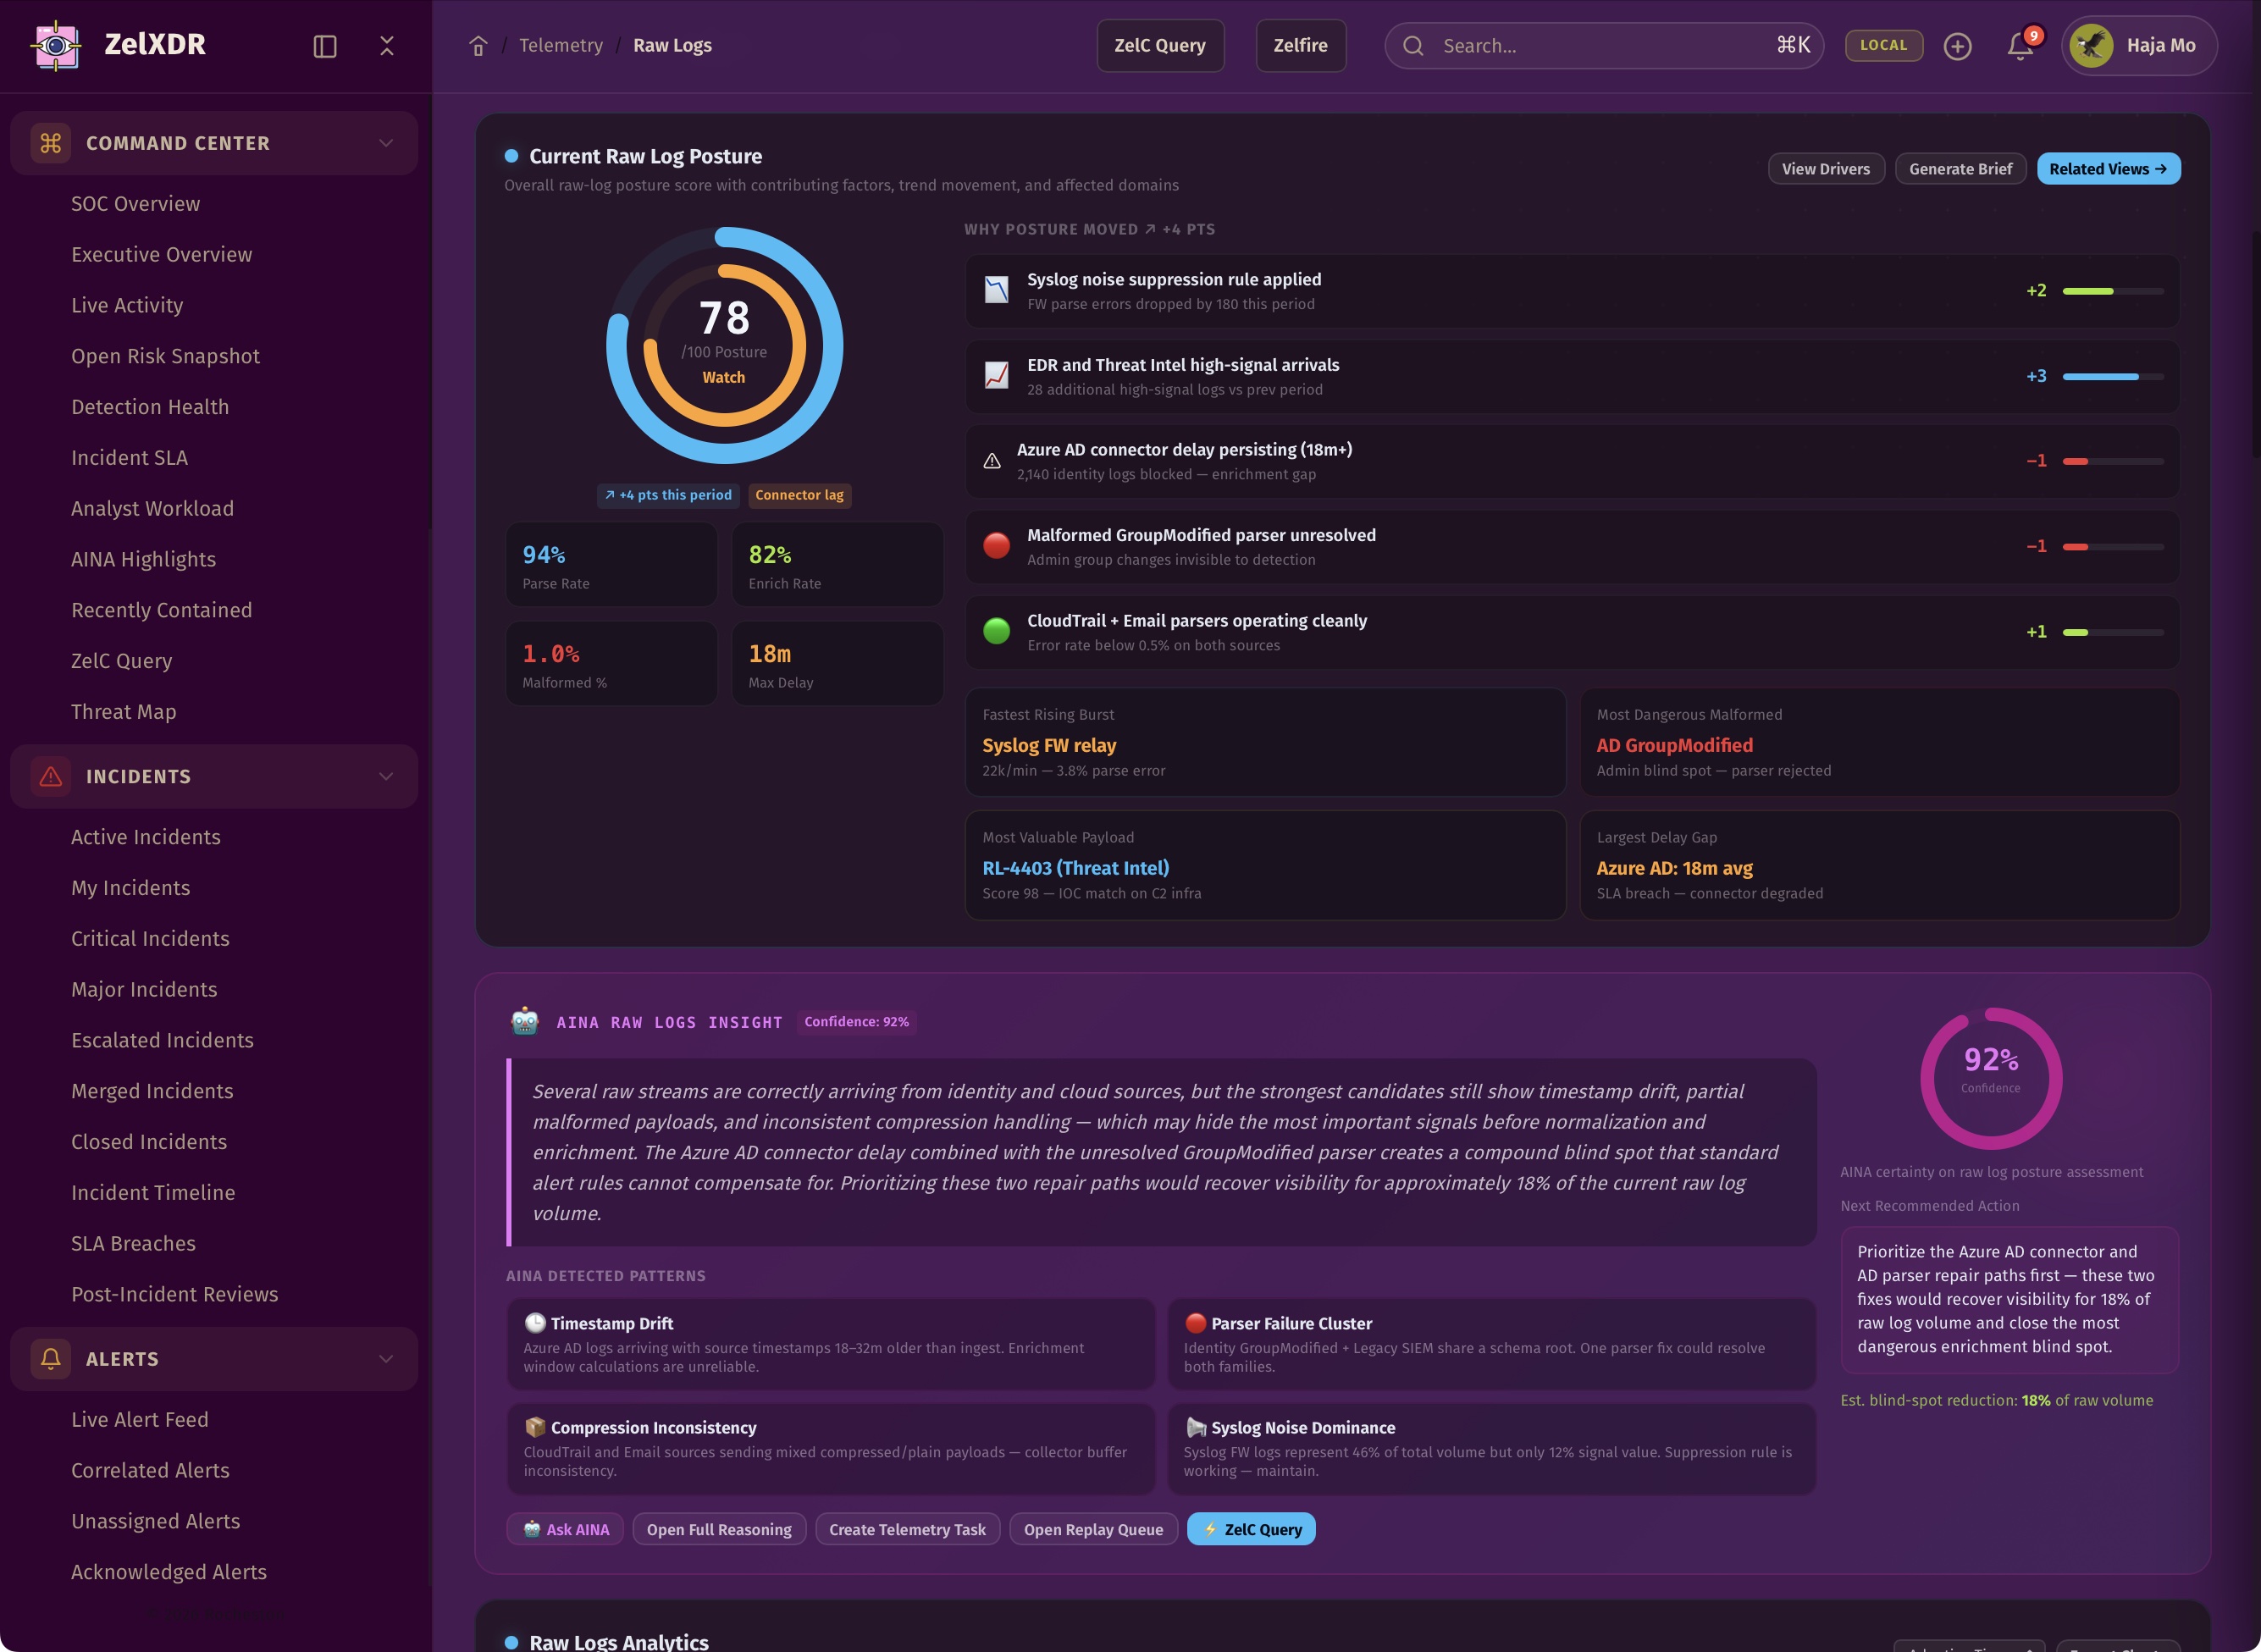
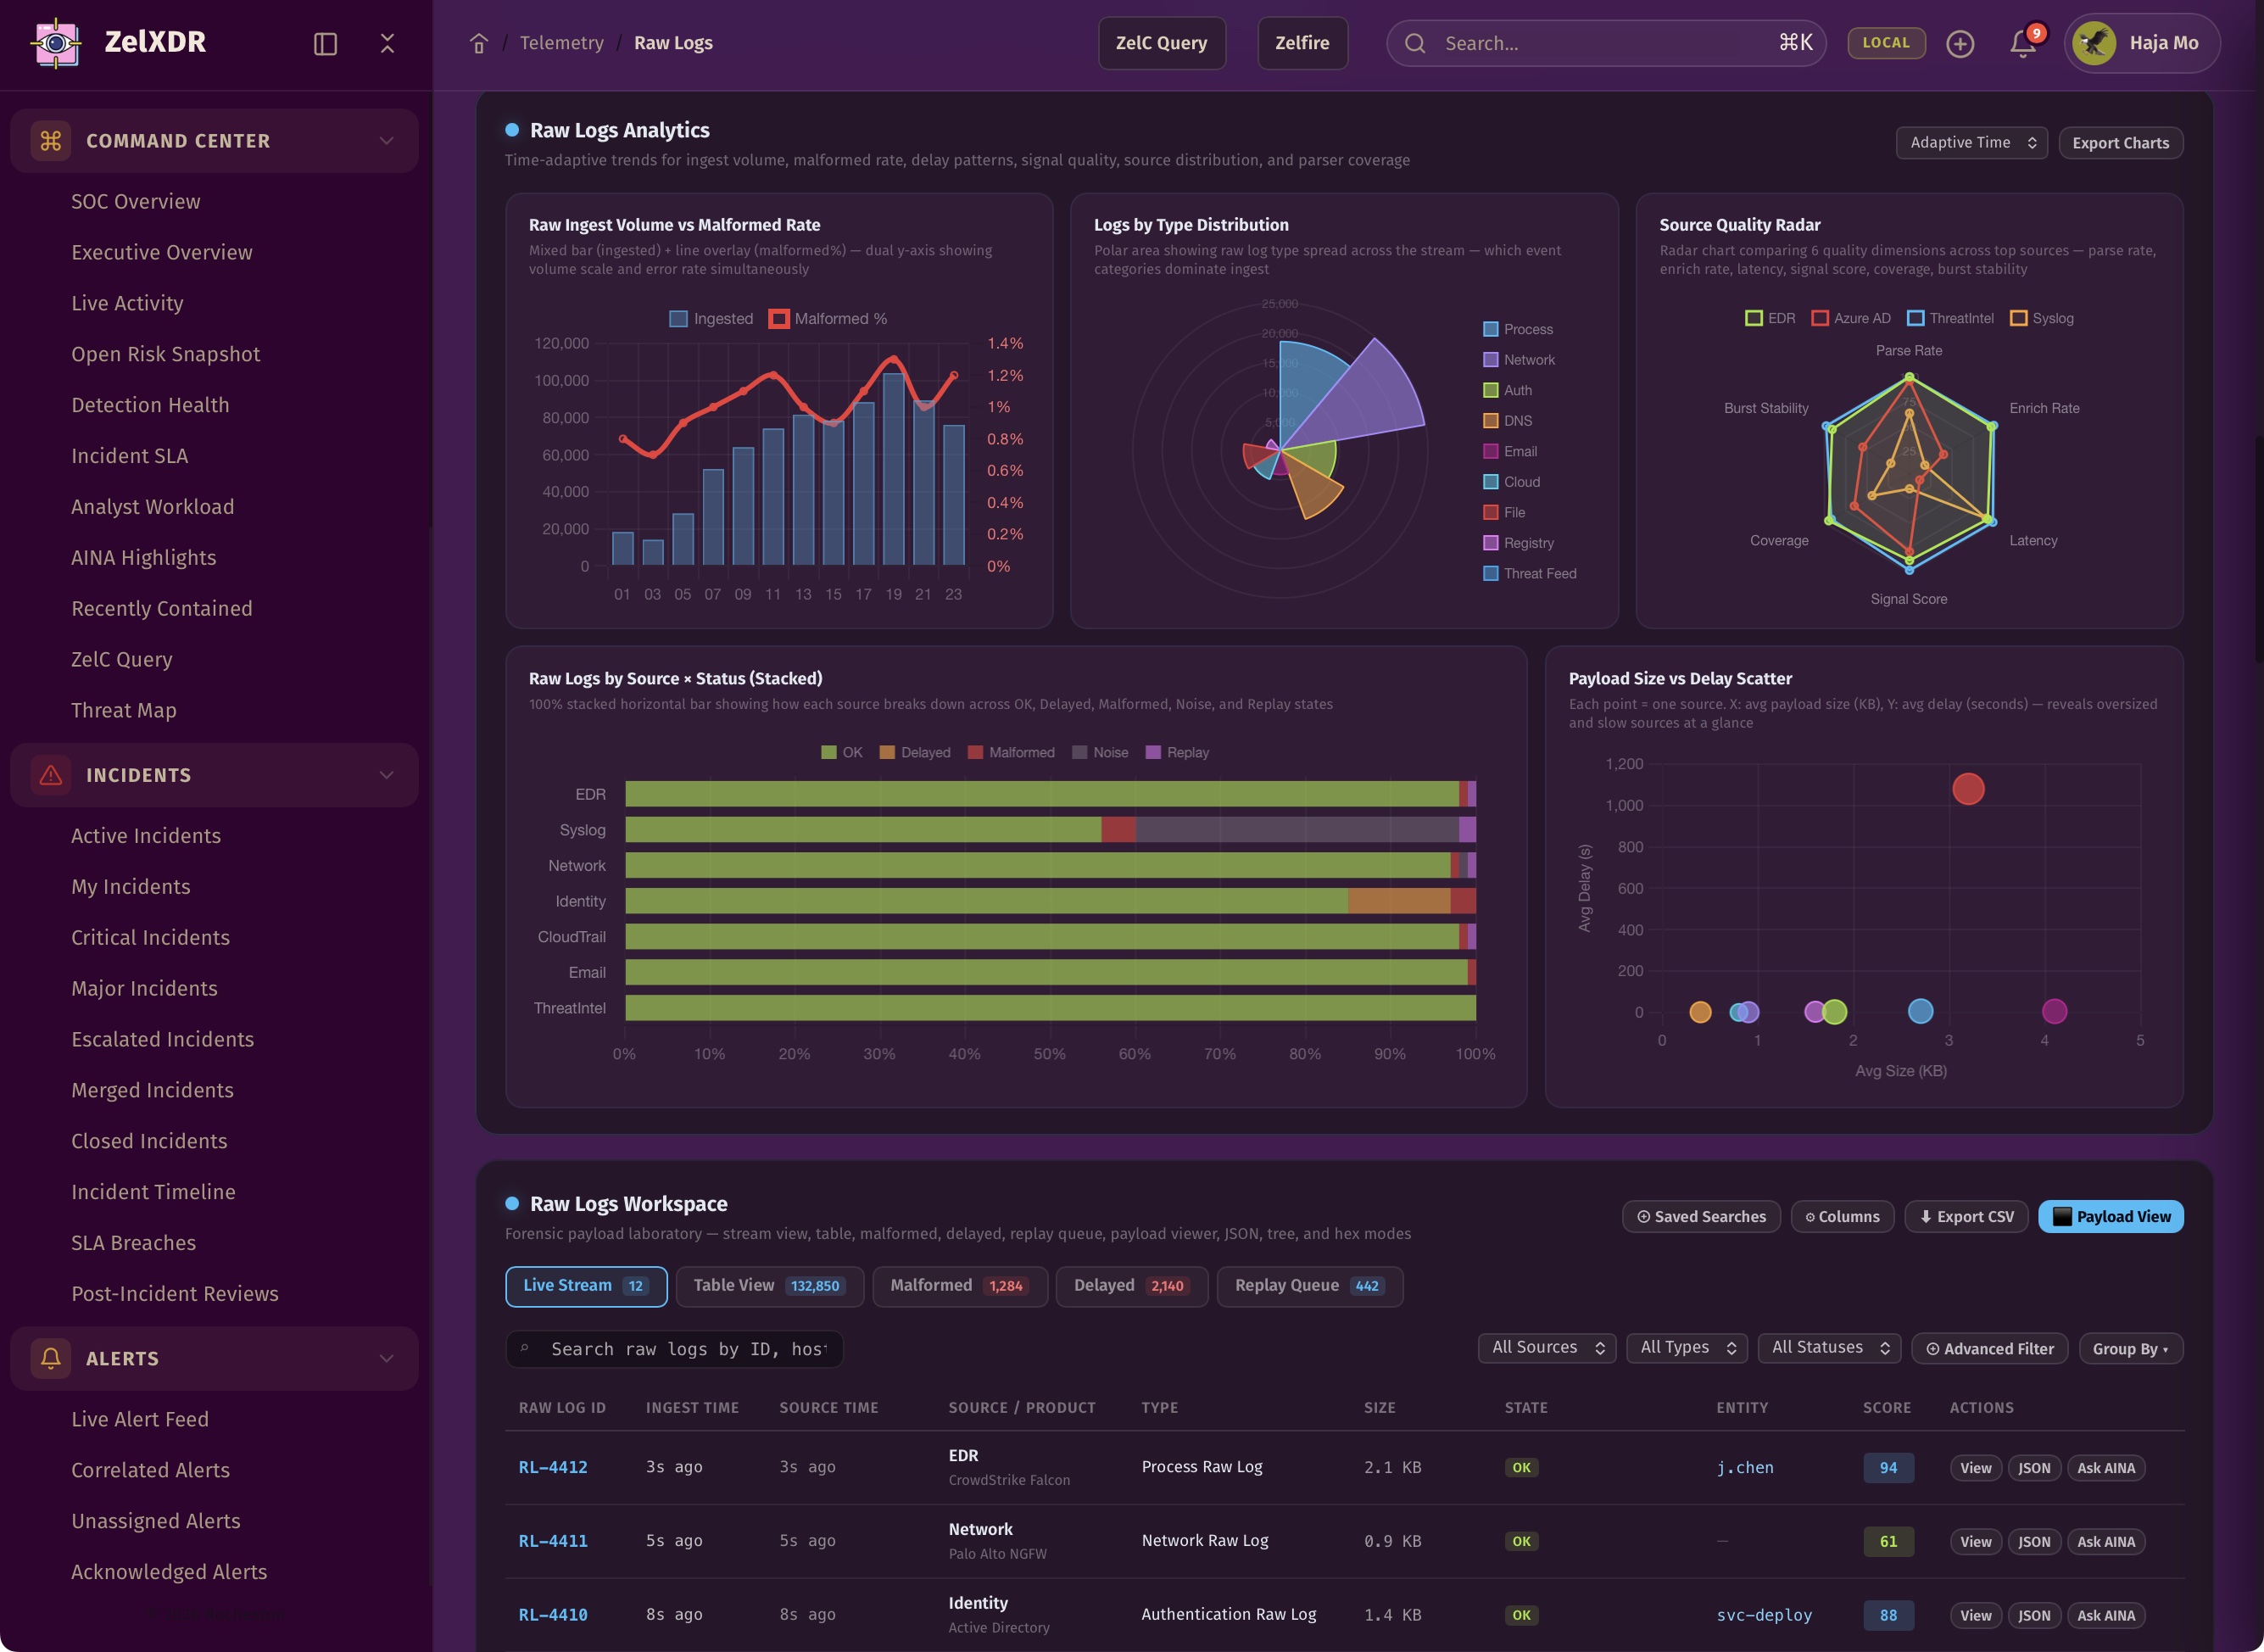
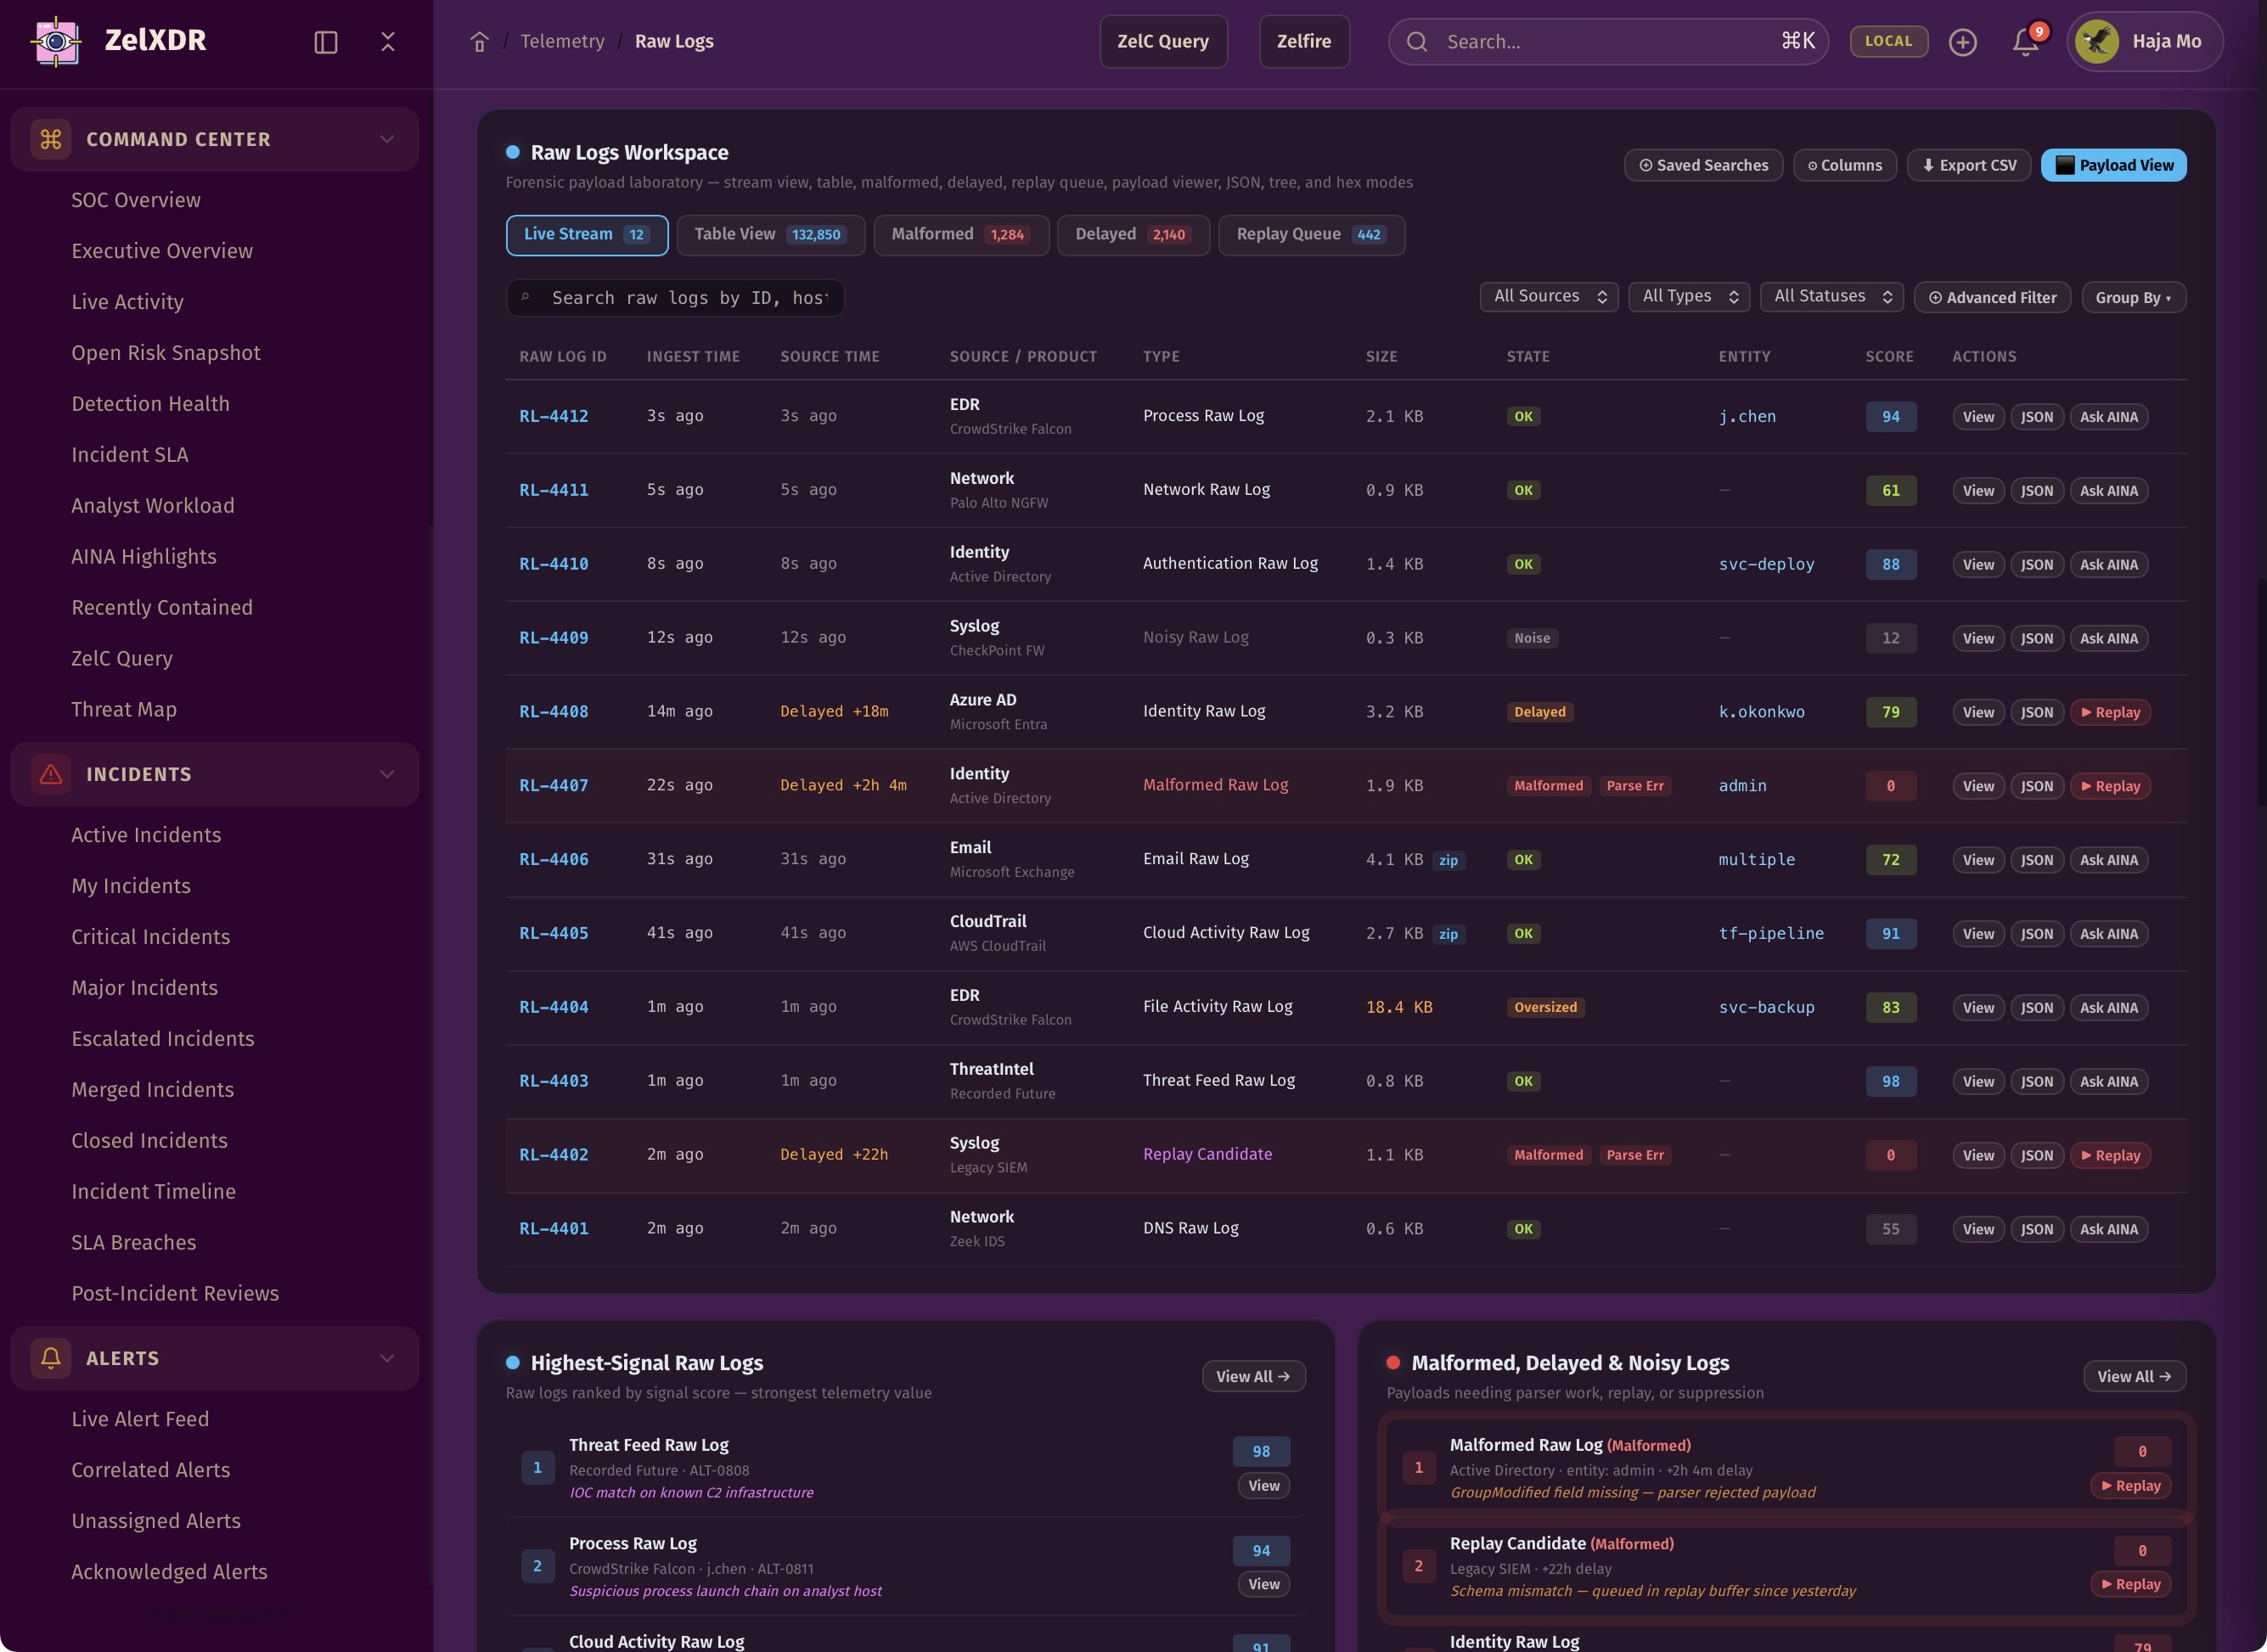
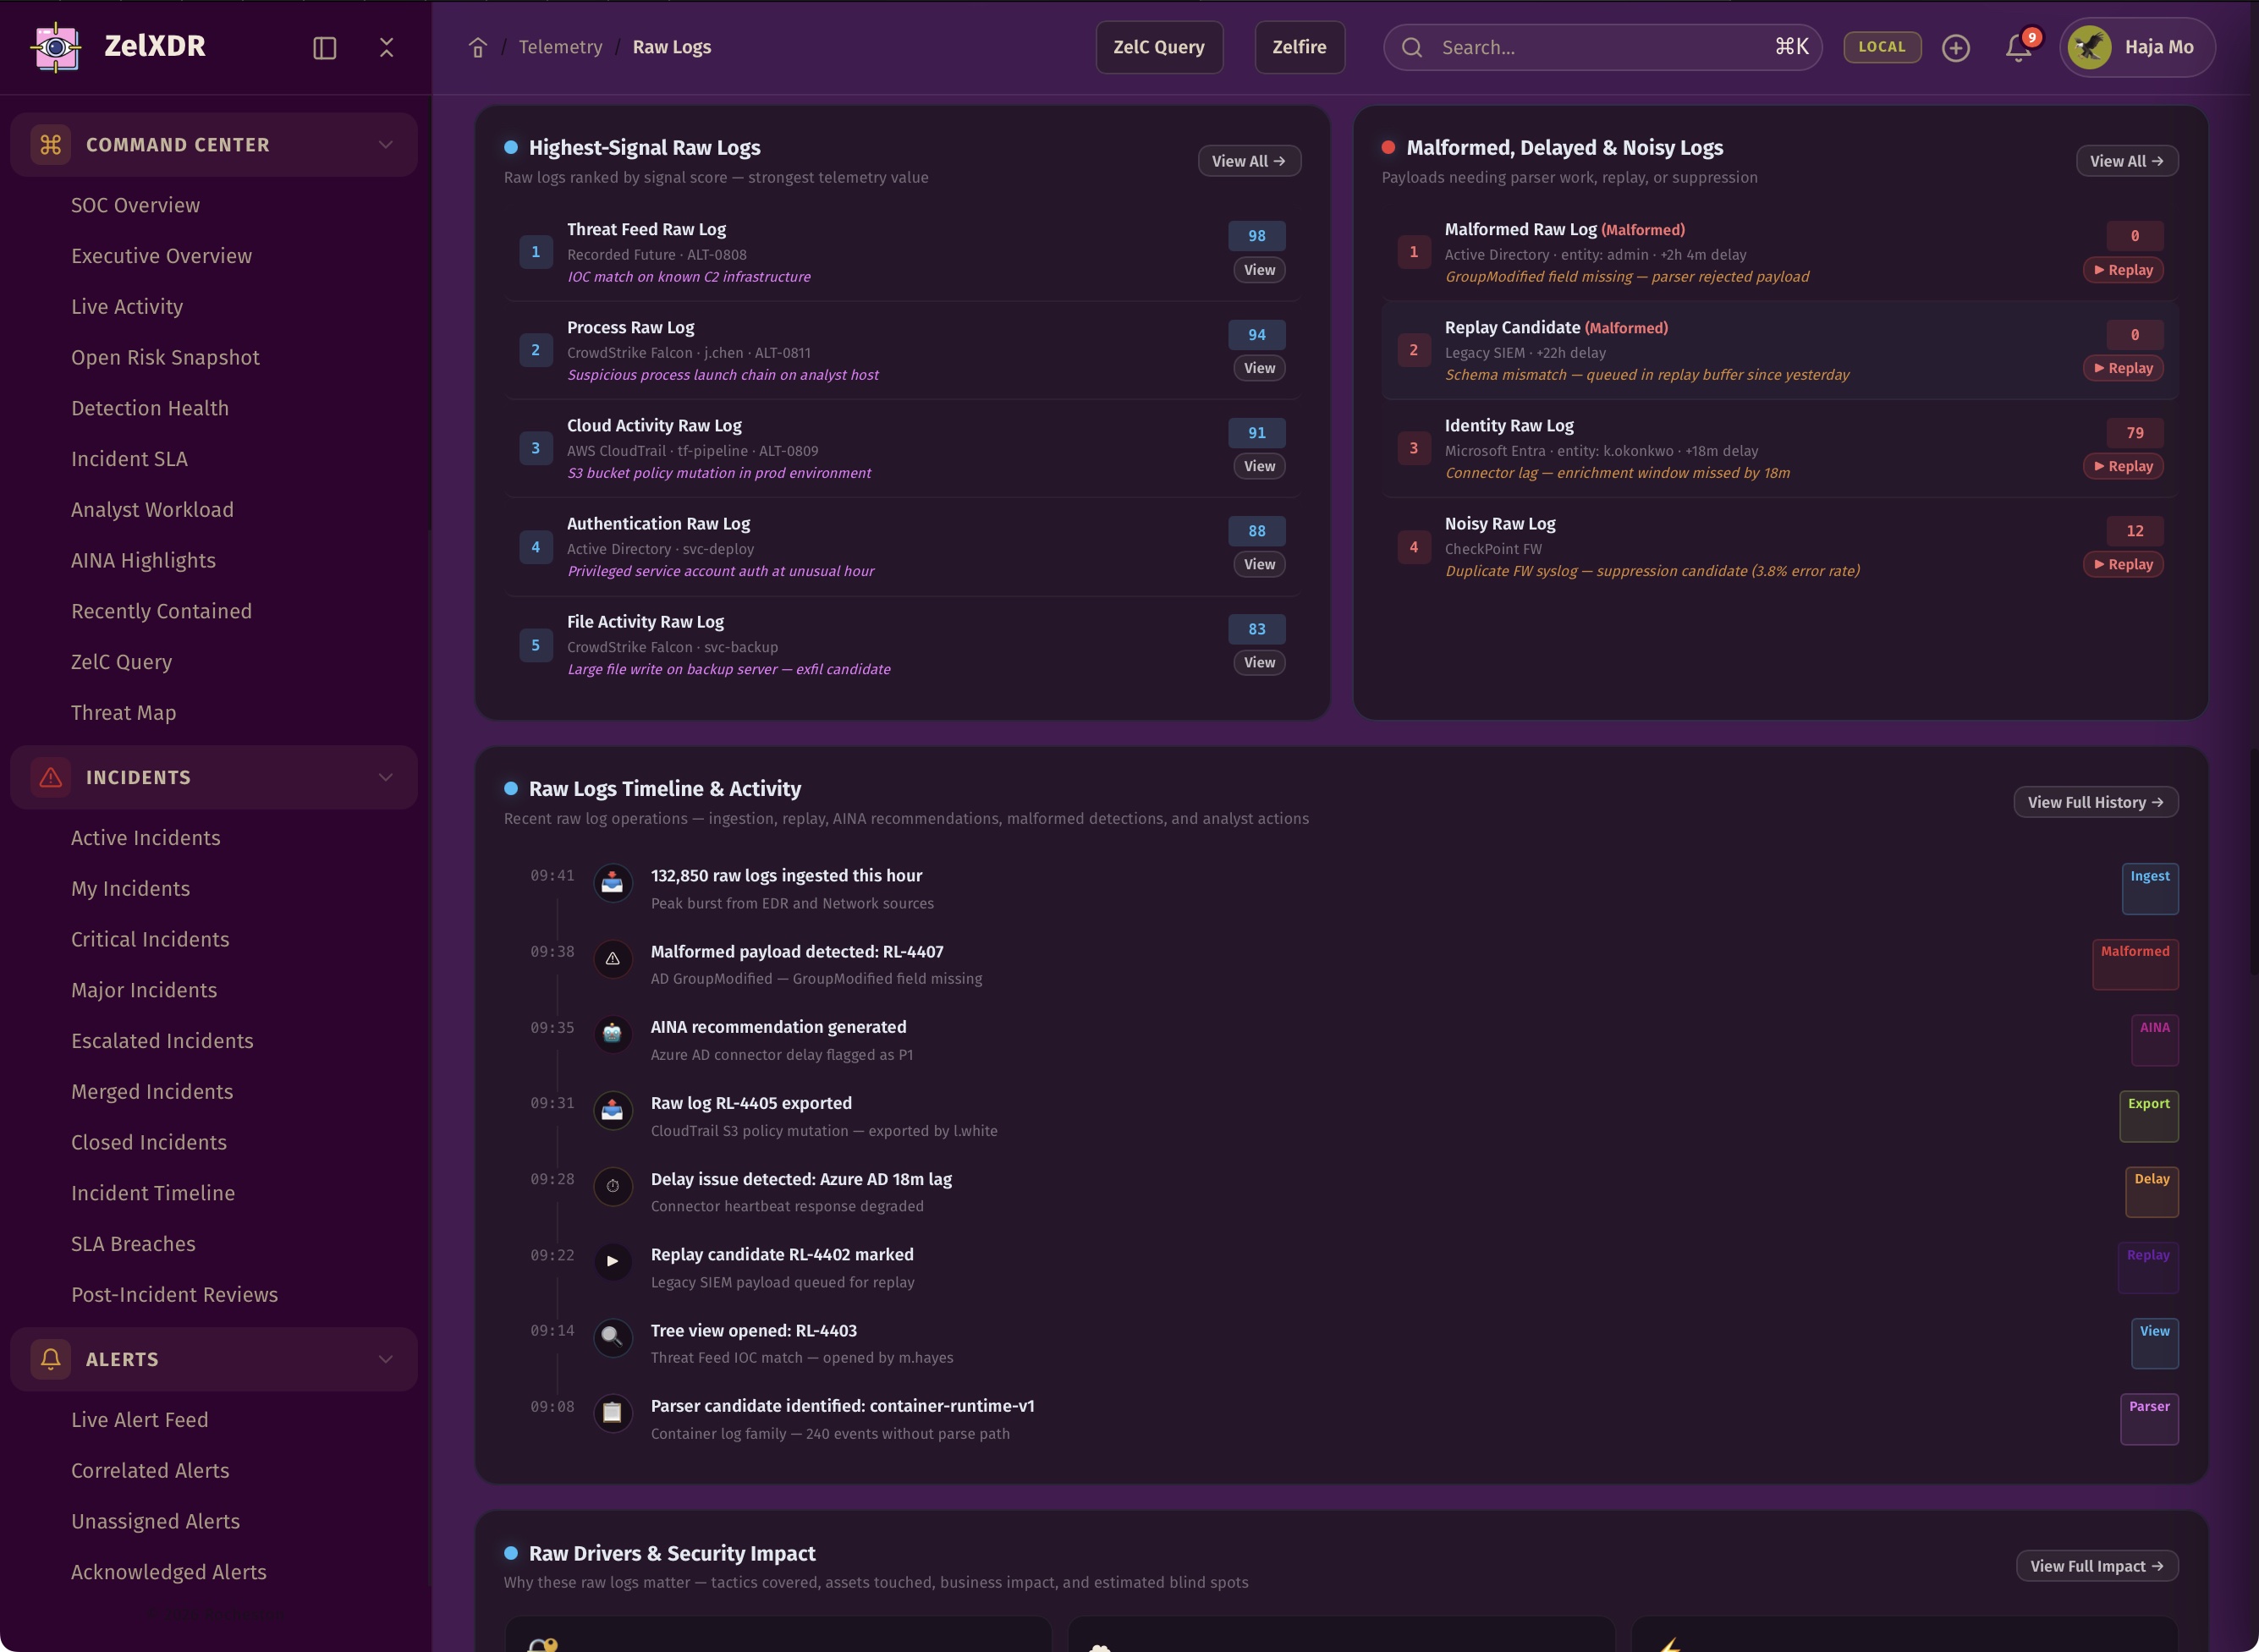
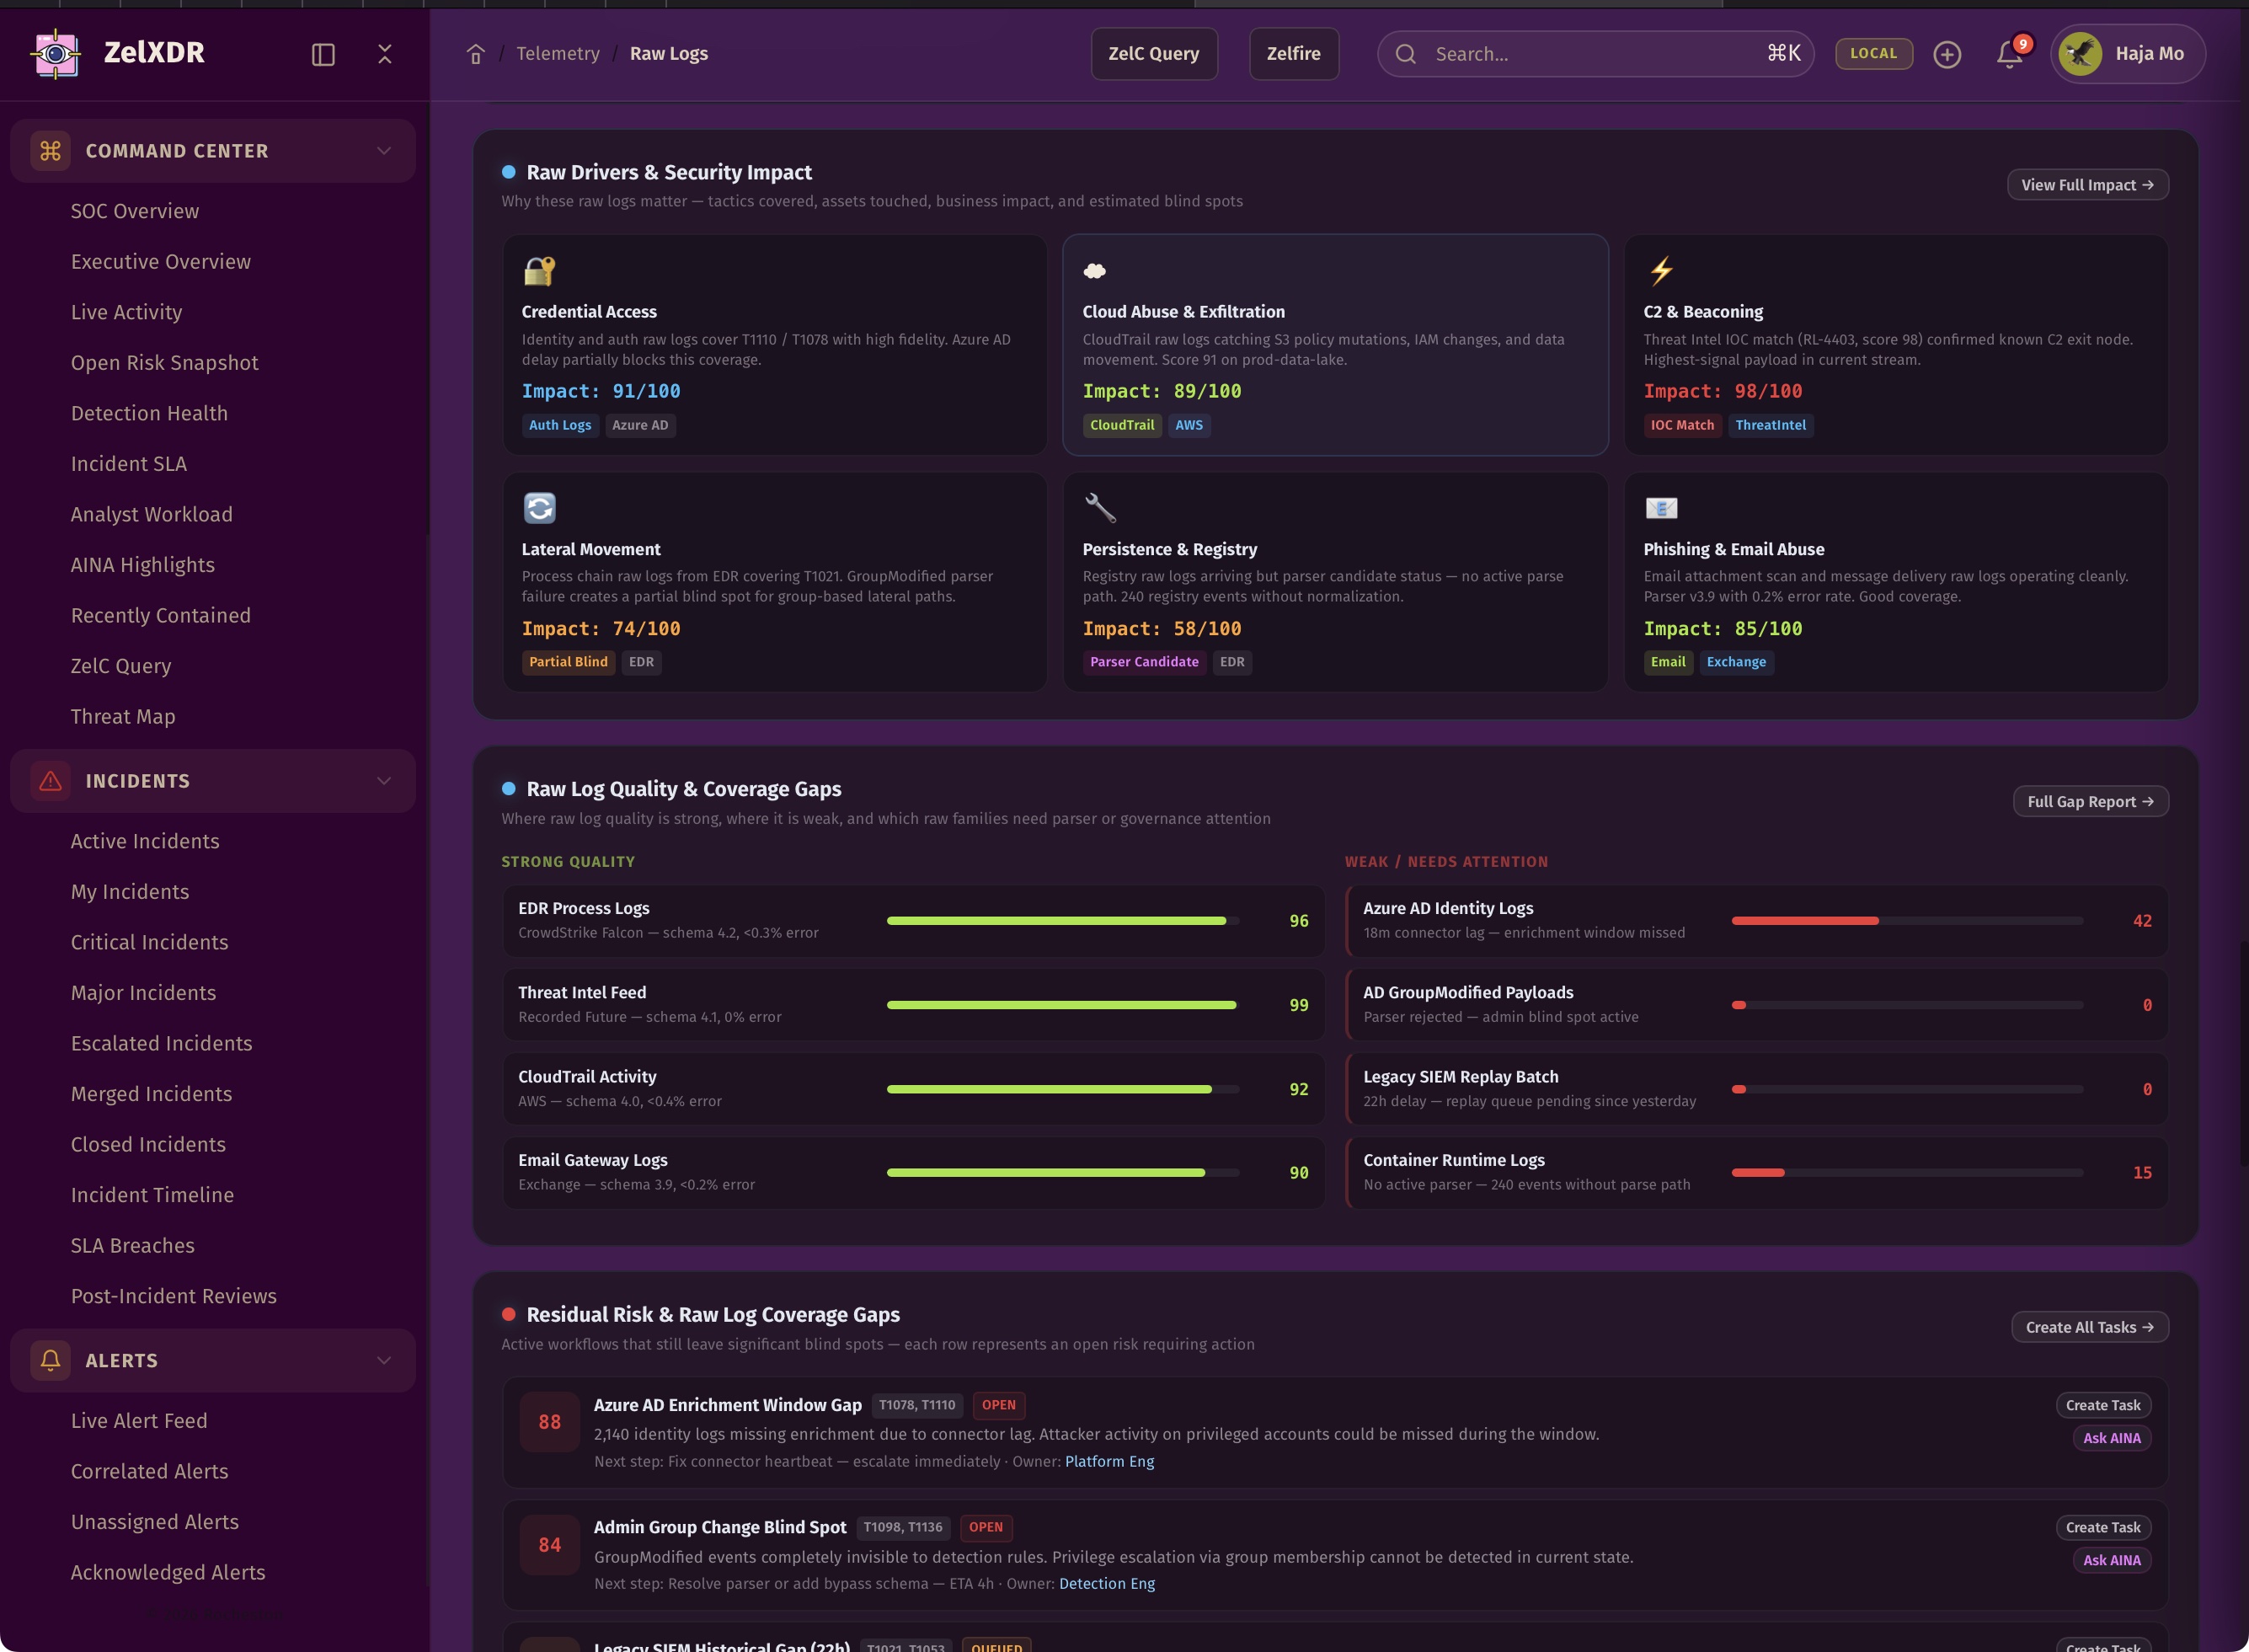
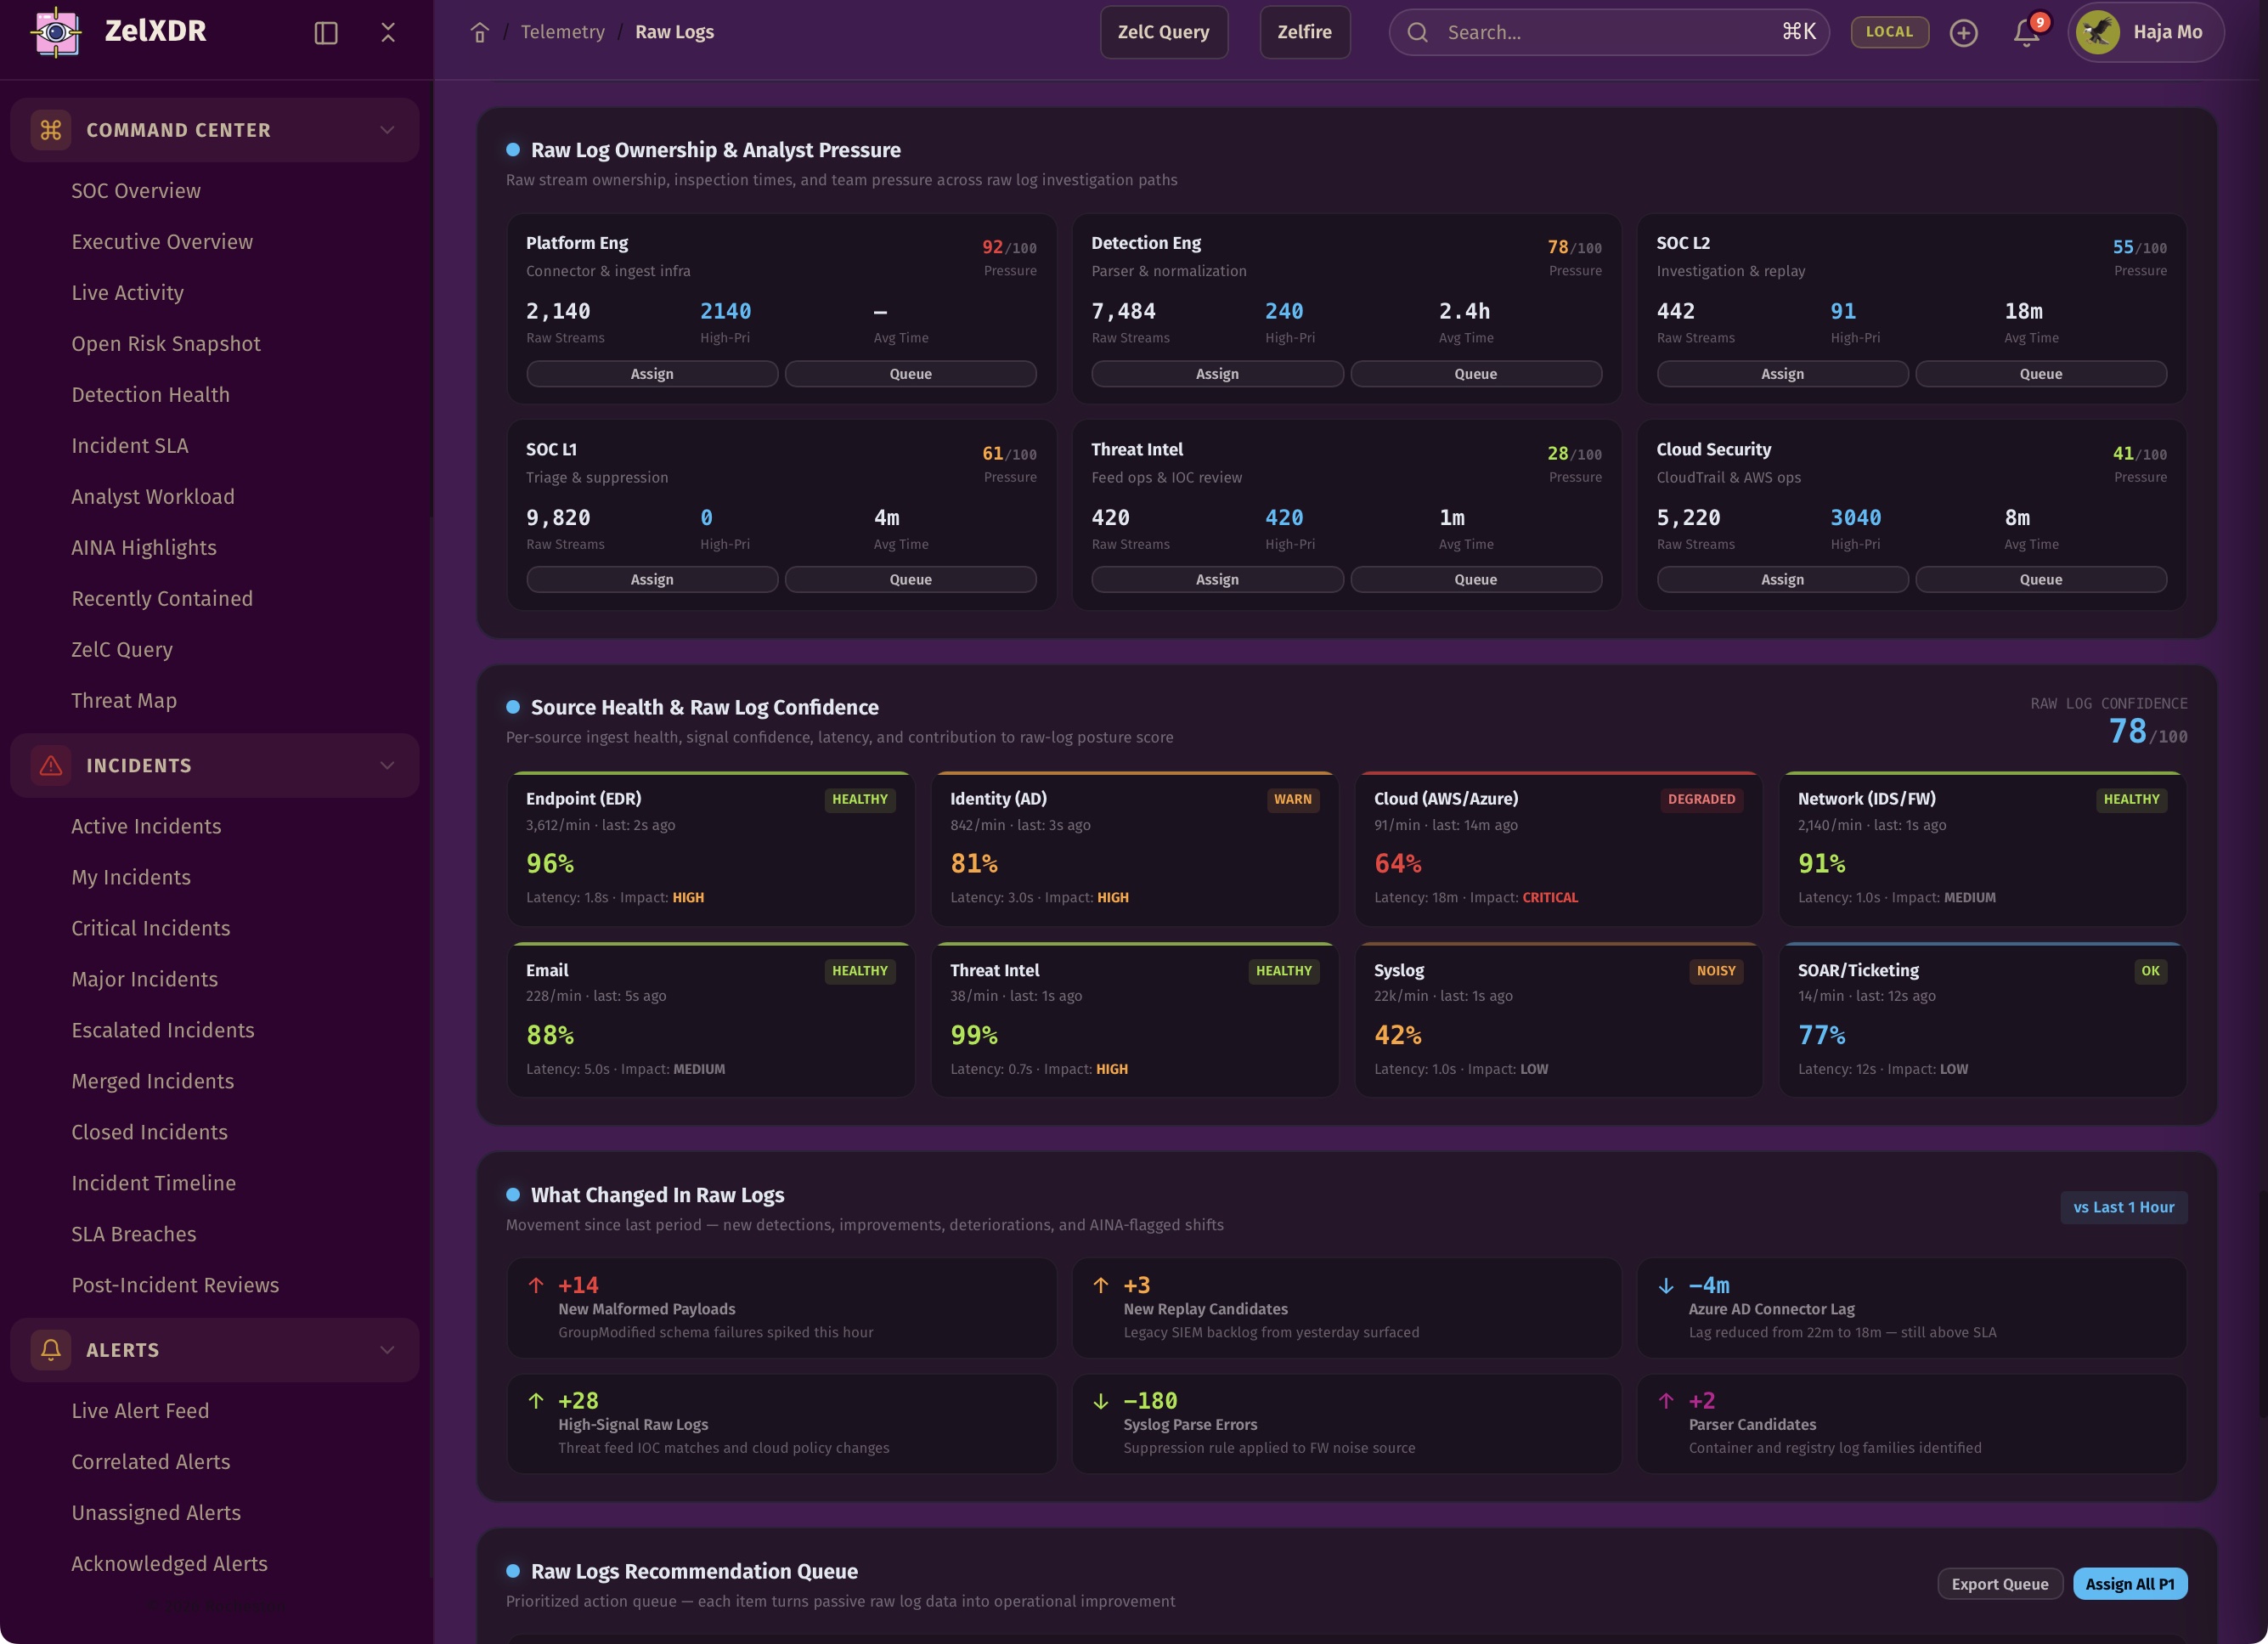
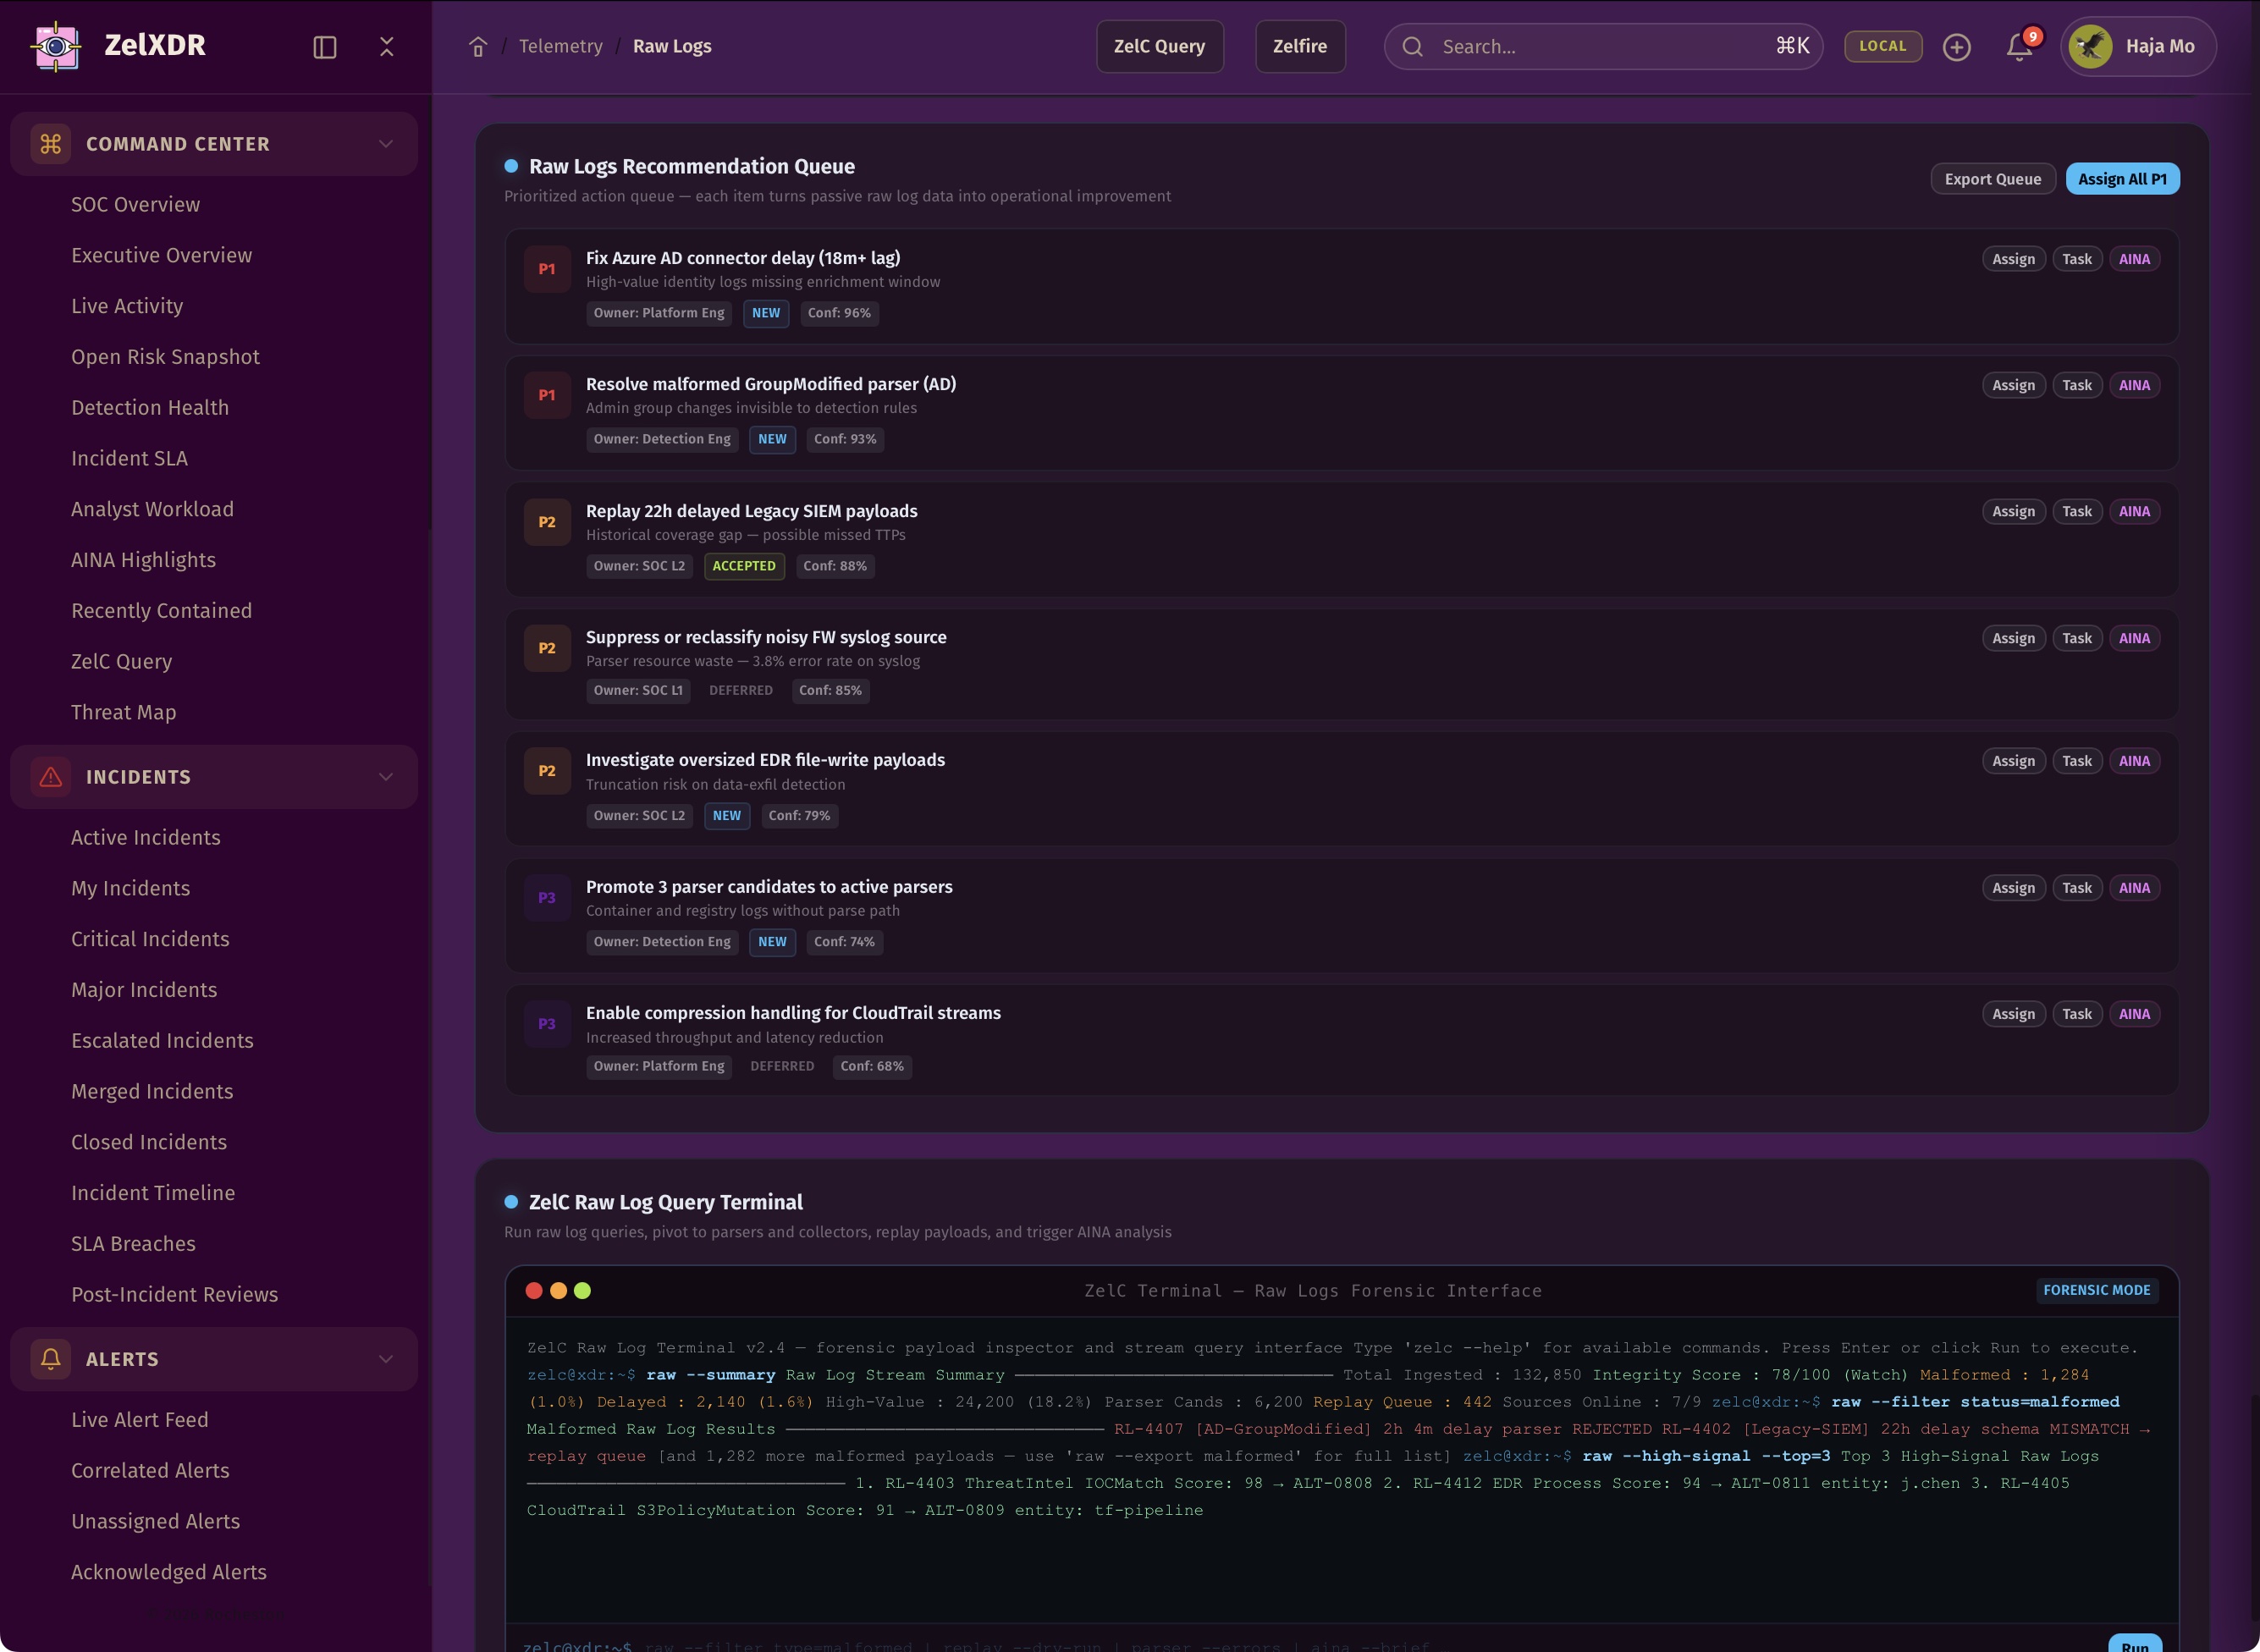
ZelXDR preserves access to original telemetry payloads so teams can inspect source-native logs, malformed records, delays, duplication, and payload structure before normalization and enrichment.
When the details matter, raw truth matters most.
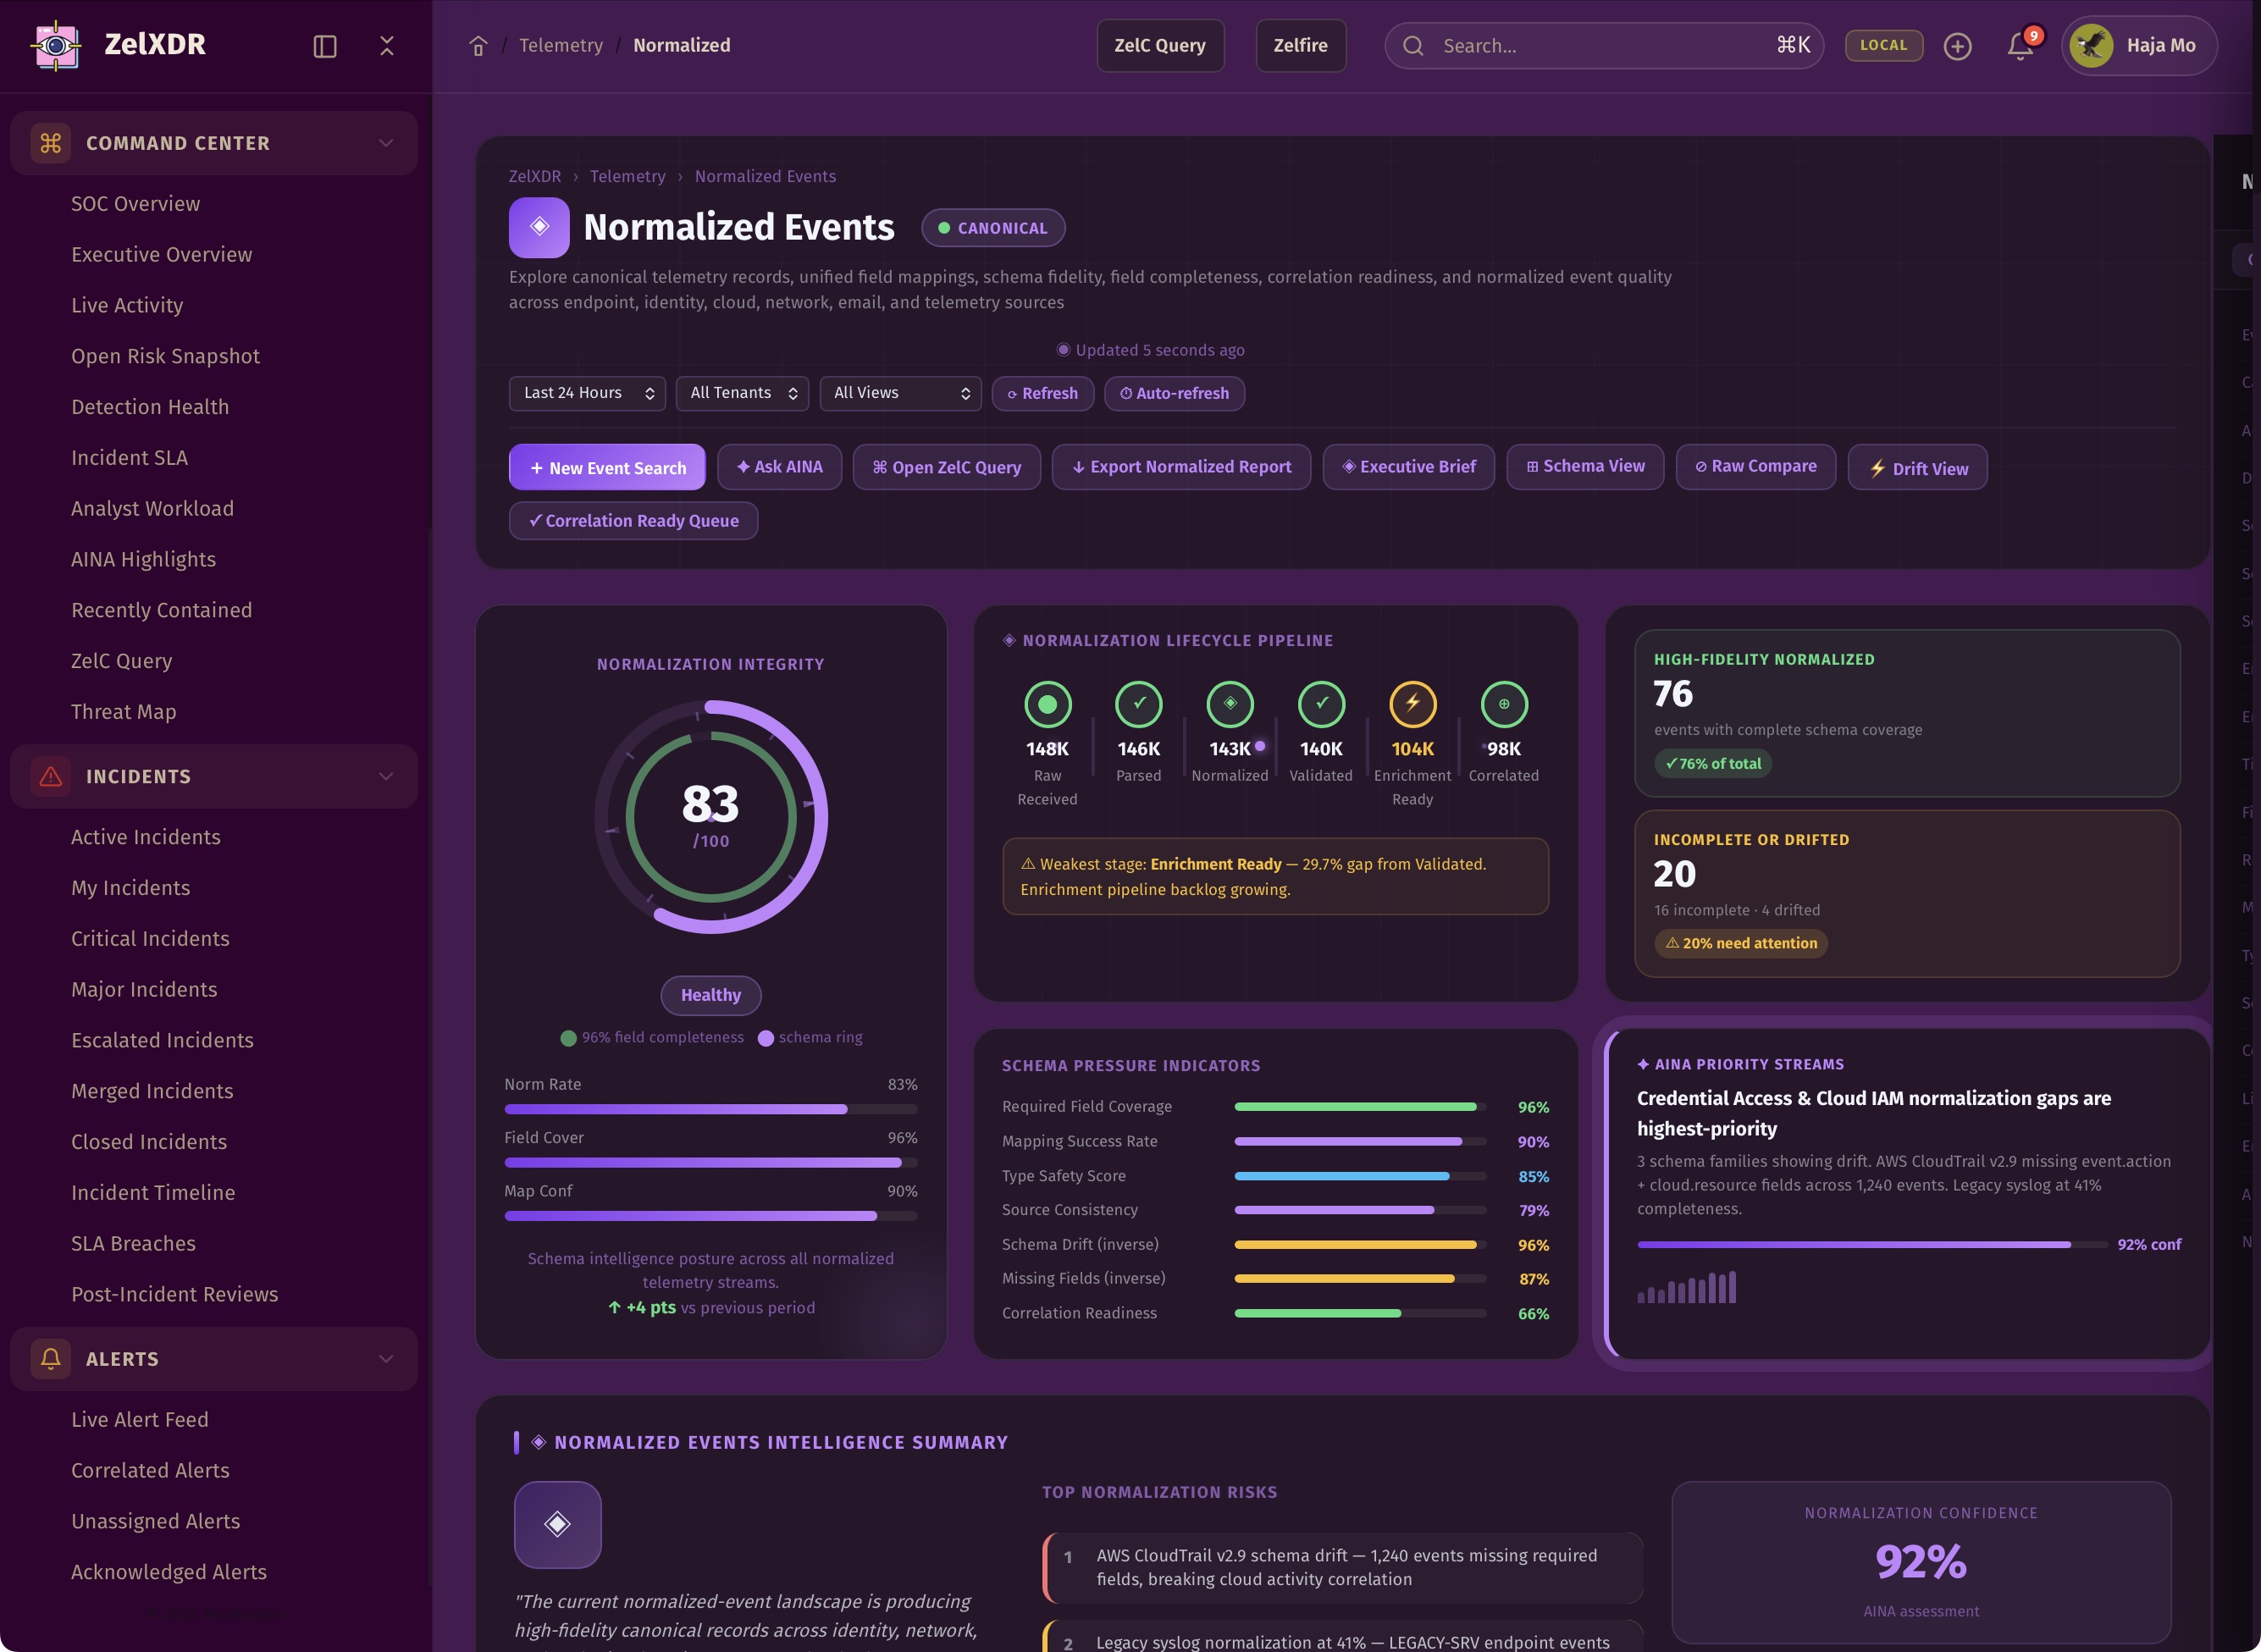
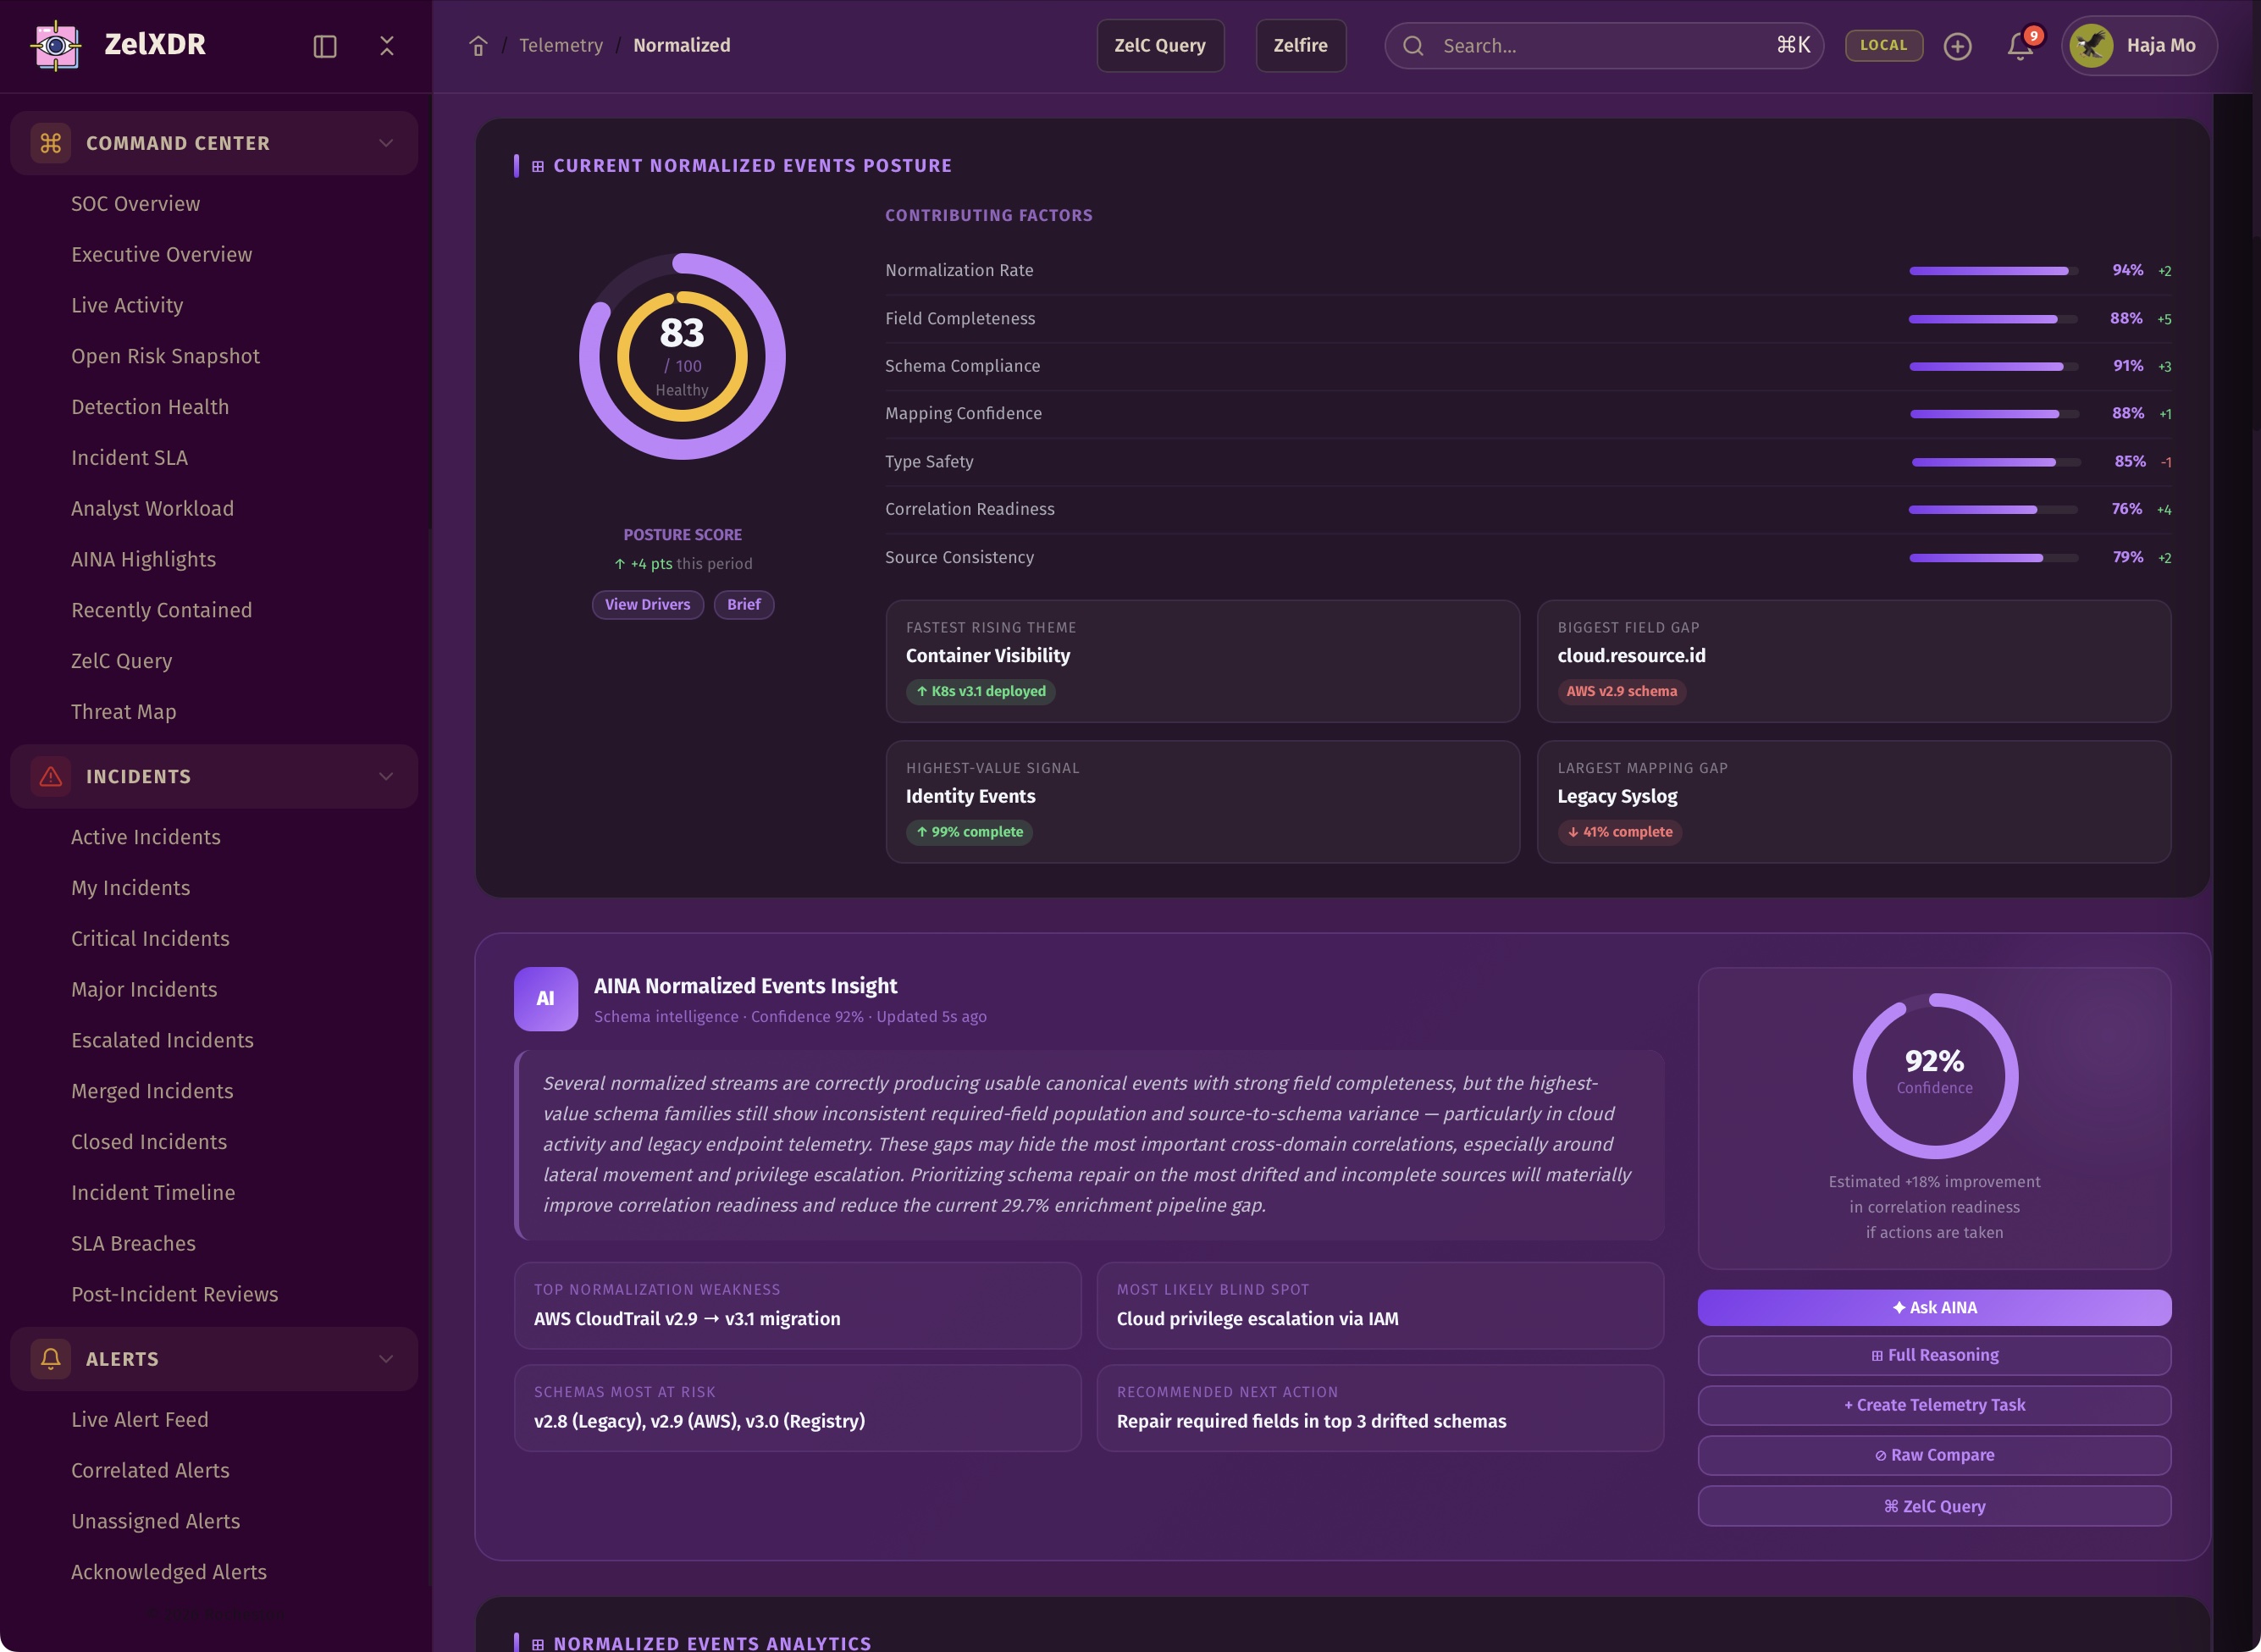
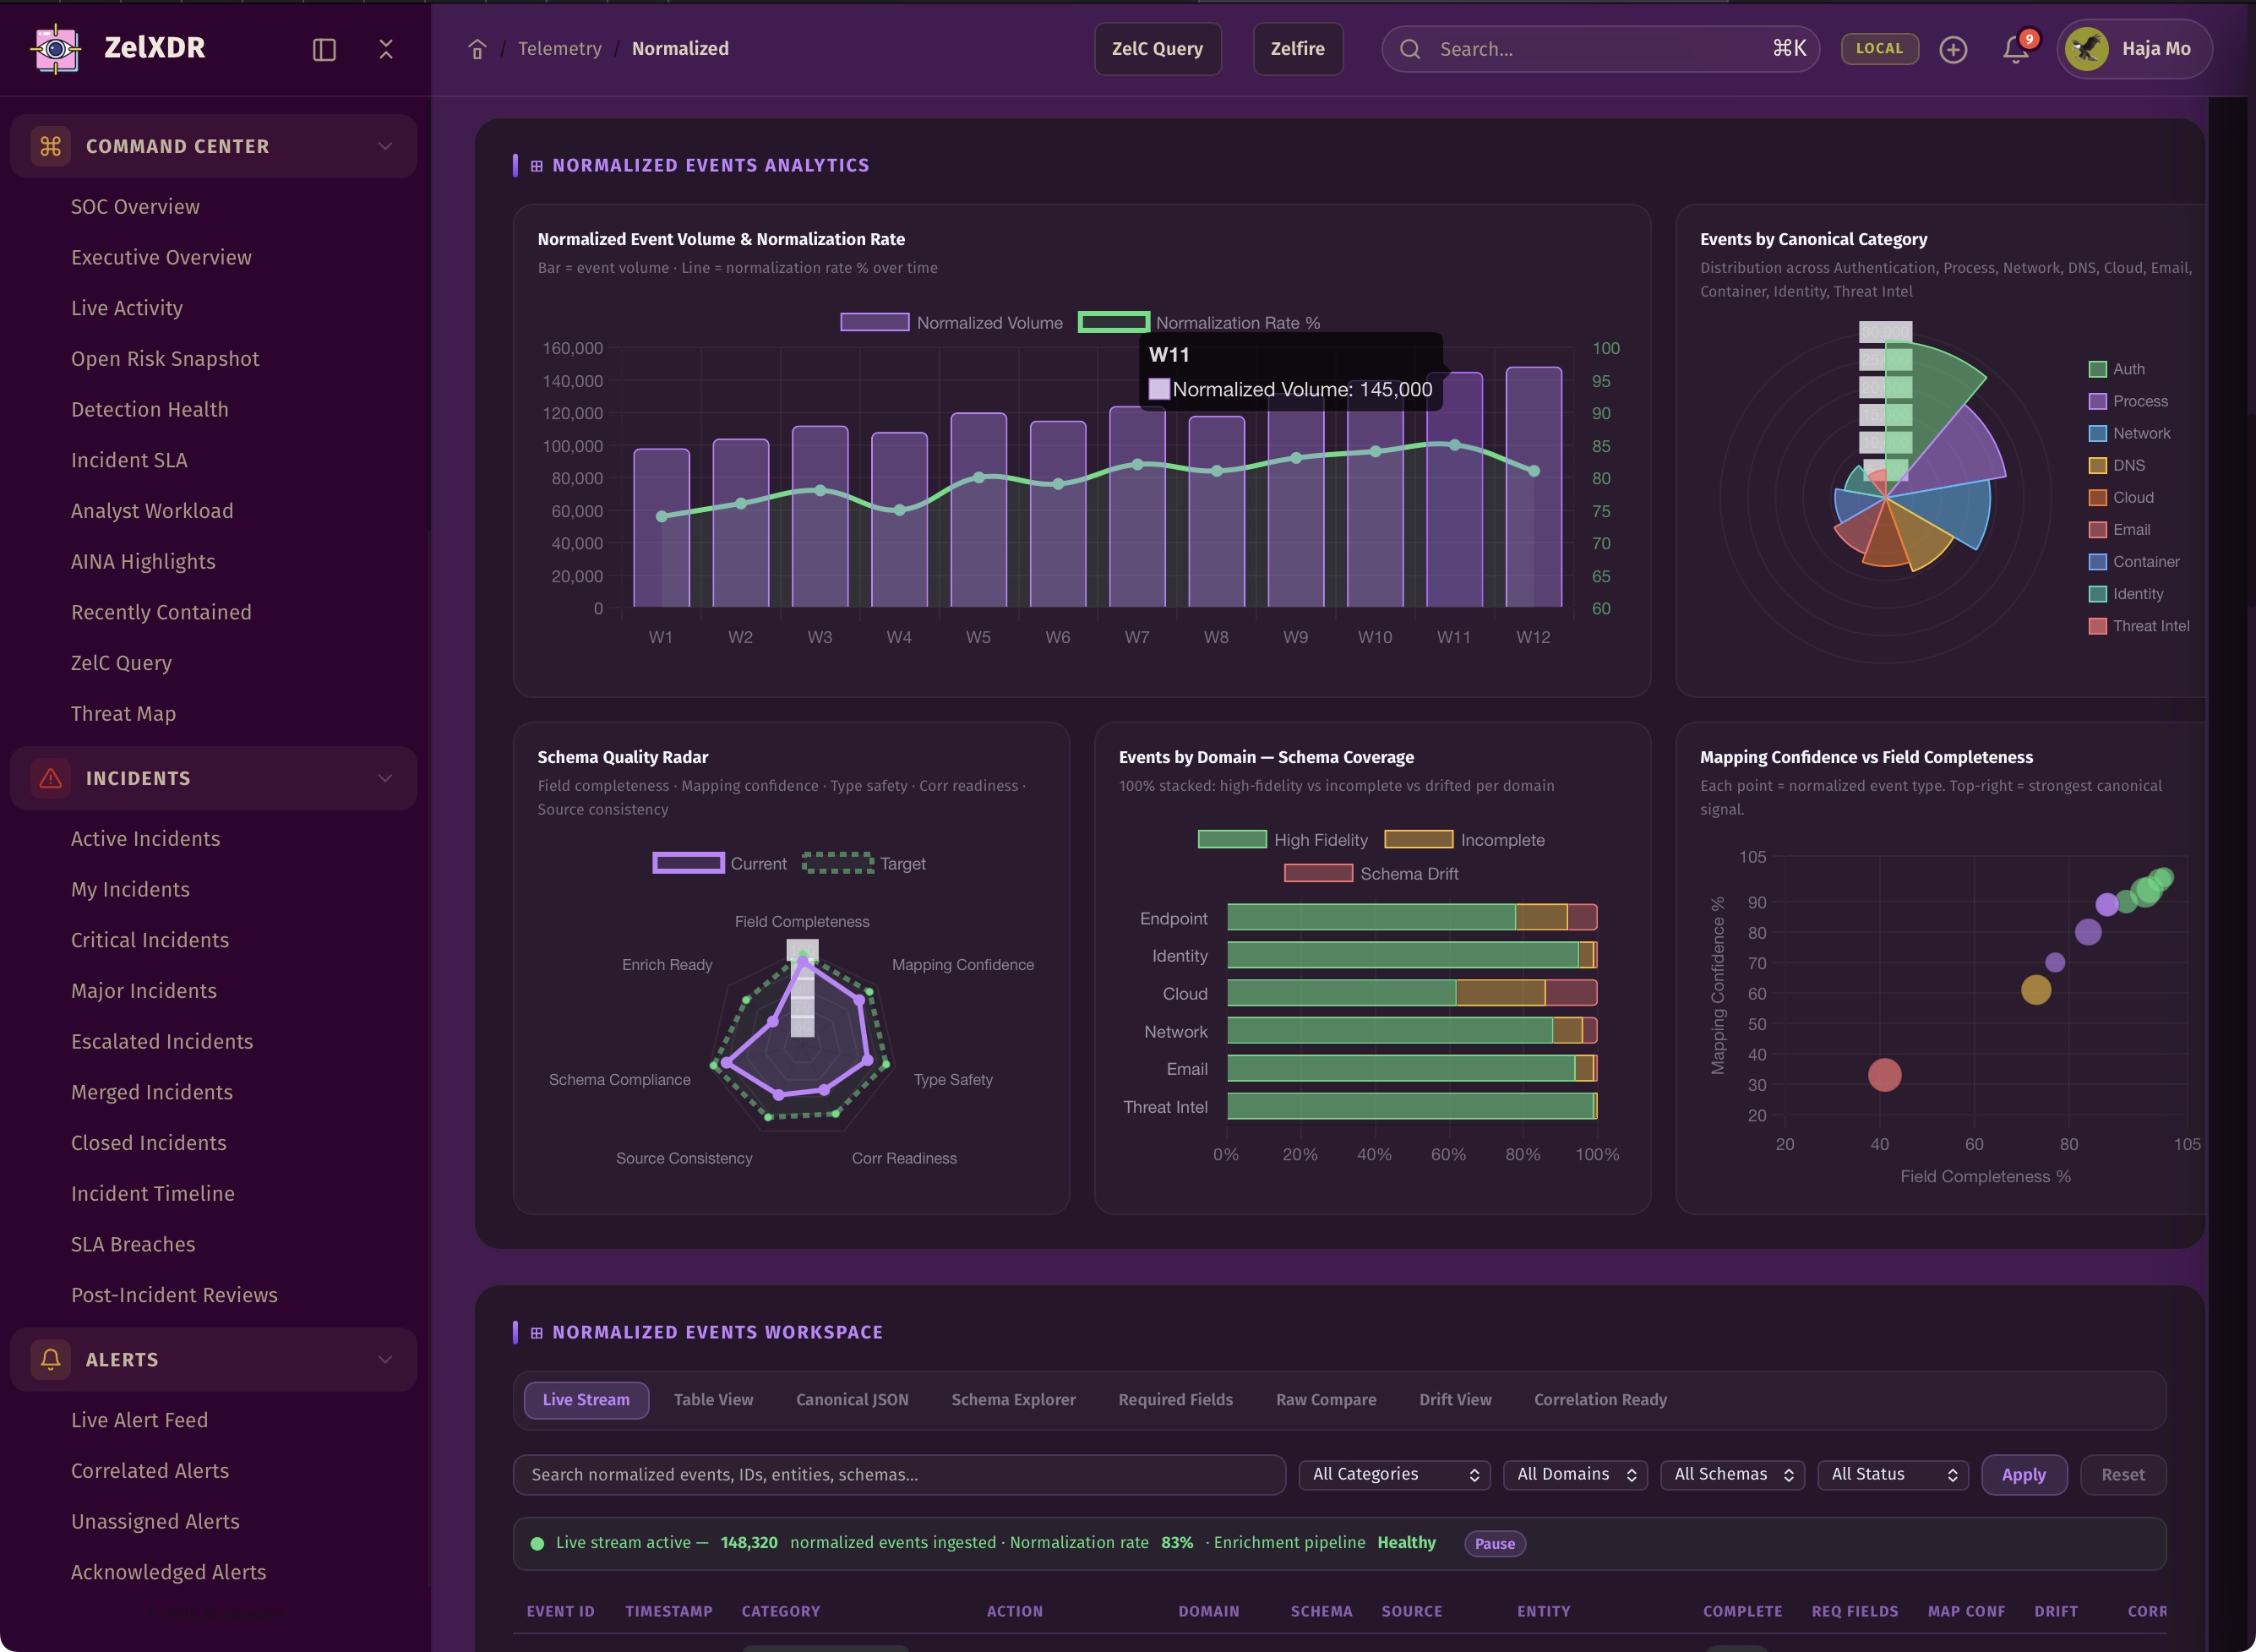
ZelXDR transforms raw logs into structured, consistent, queryable events. This creates a stable foundation for enrichment, hunting, detection logic, analytics, and cross-domain investigation.
Normalization is where chaos becomes searchable.
By linking events to assets, identities, threat intelligence, relationships, and platform context, ZelXDR turns basic telemetry into enriched evidence that is easier to understand and act on.
Enrichment turns data into direction.
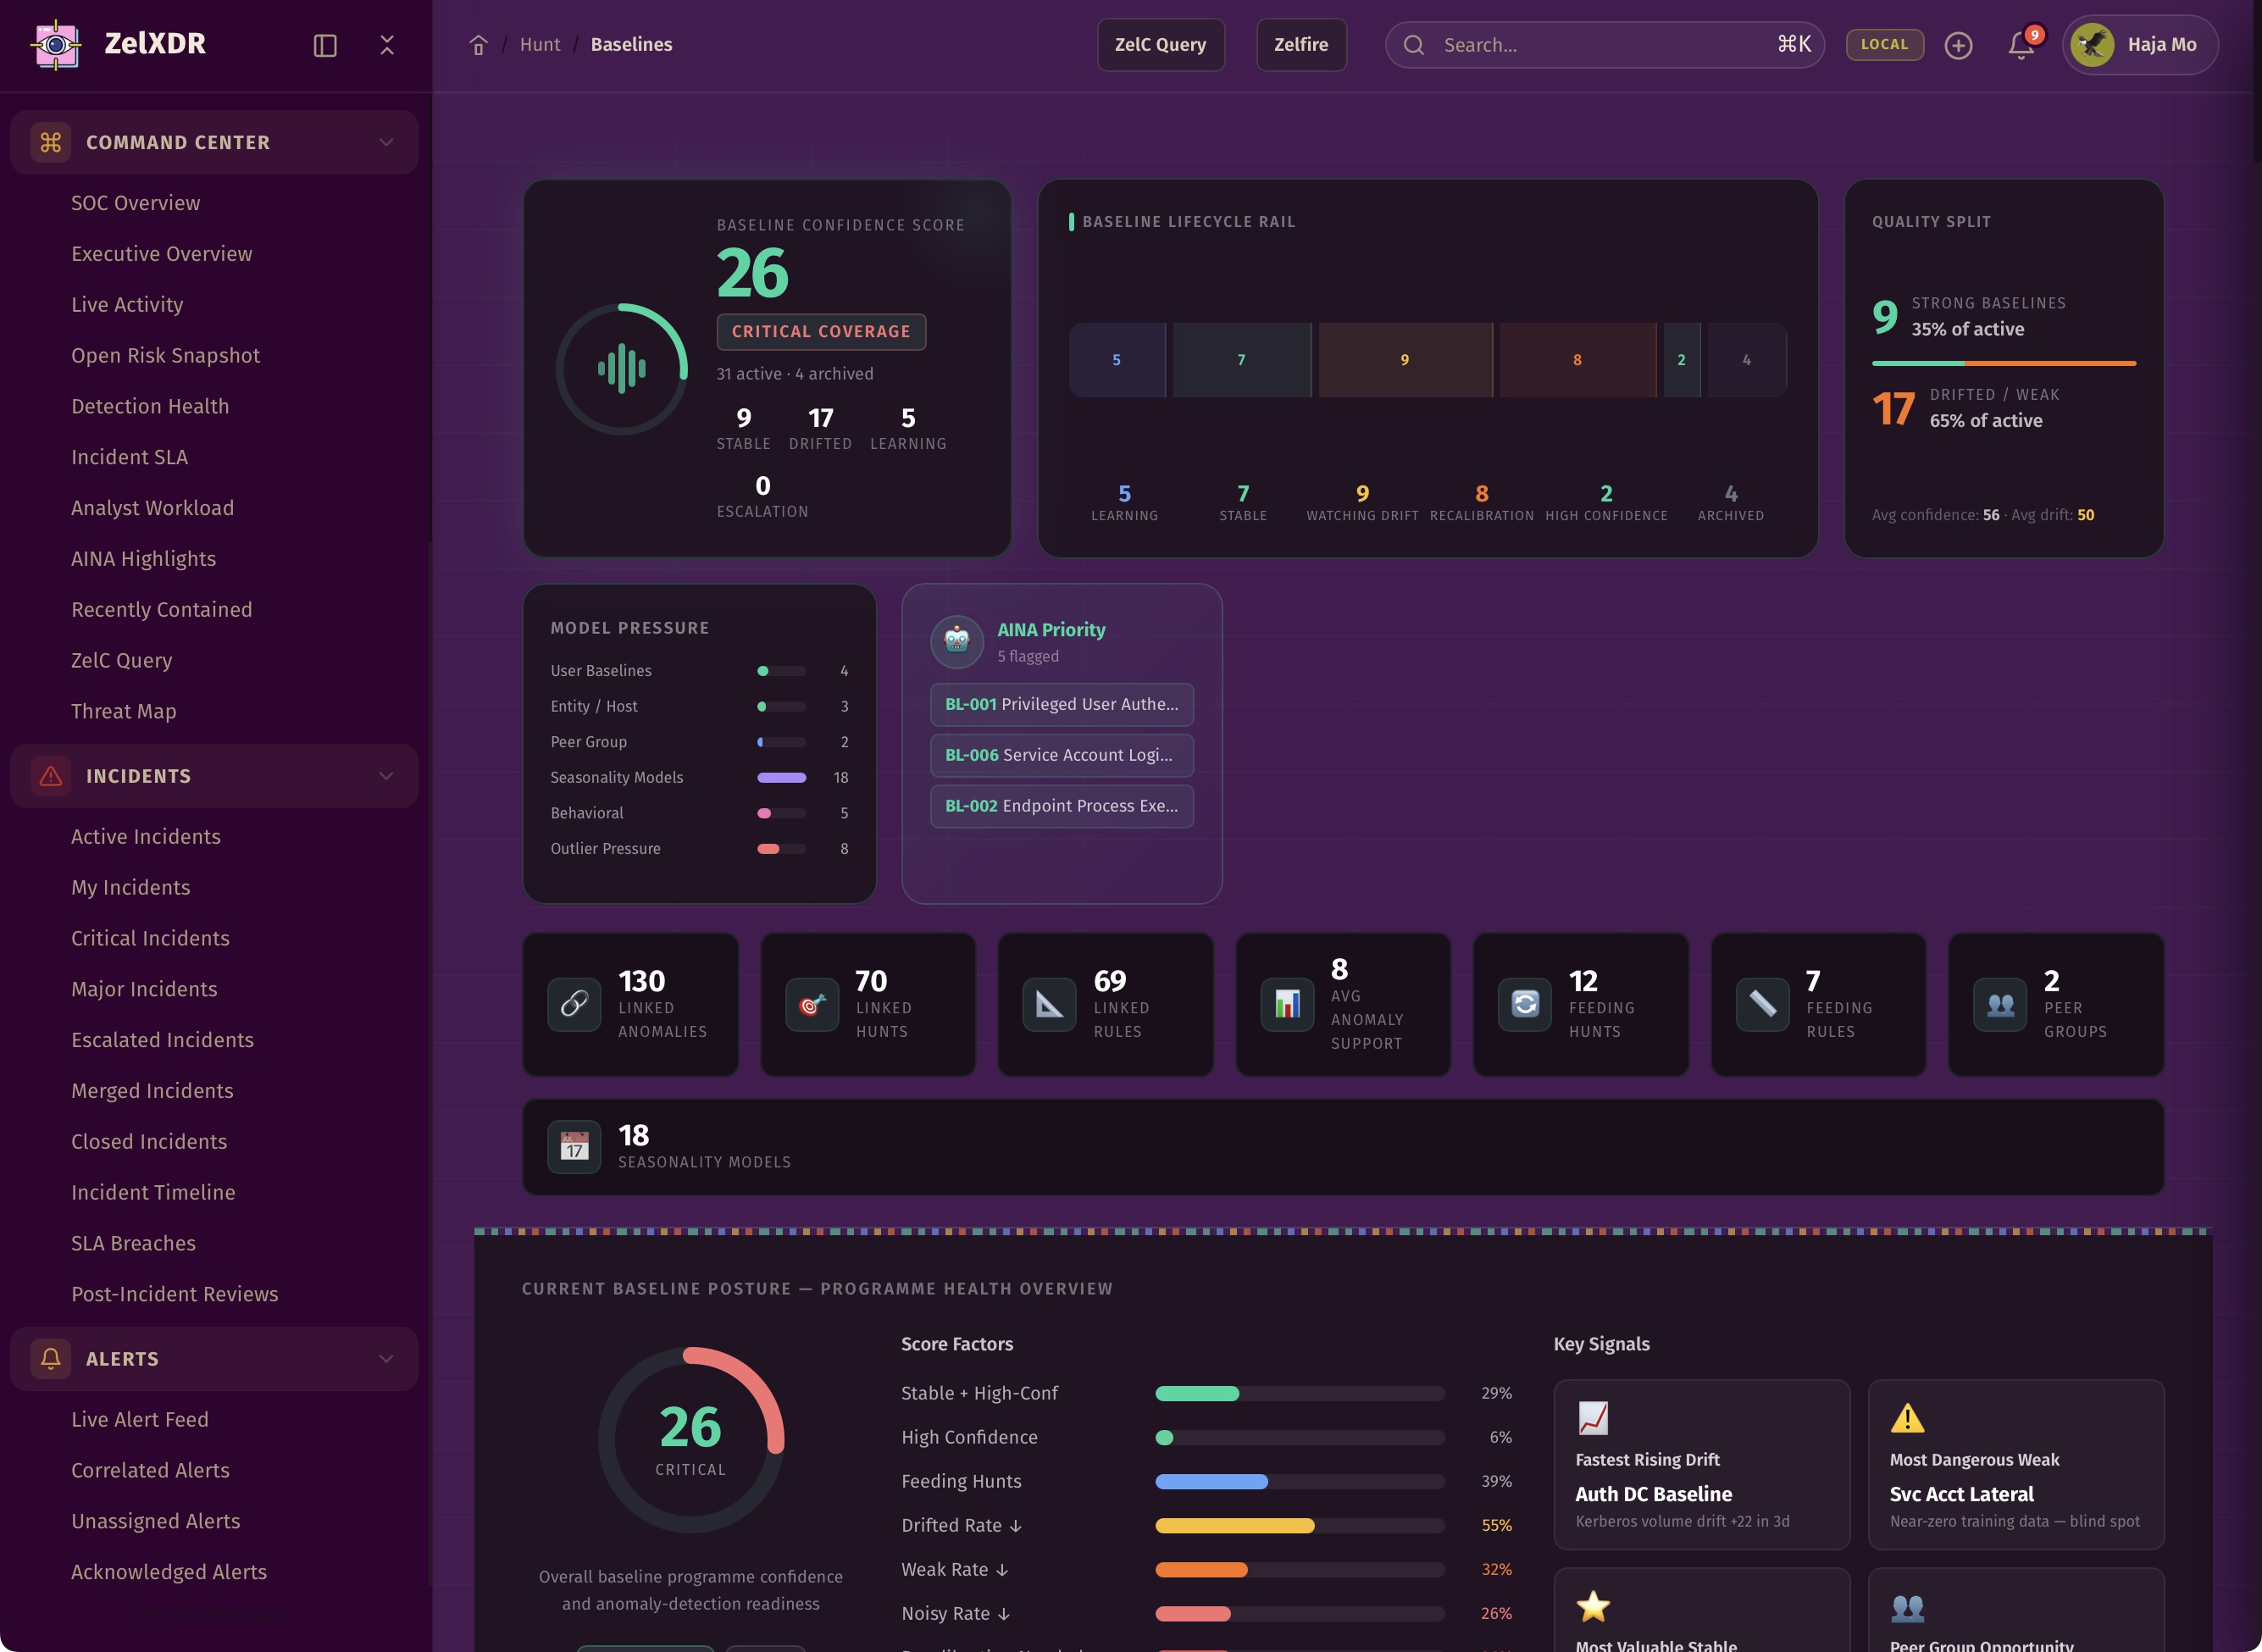
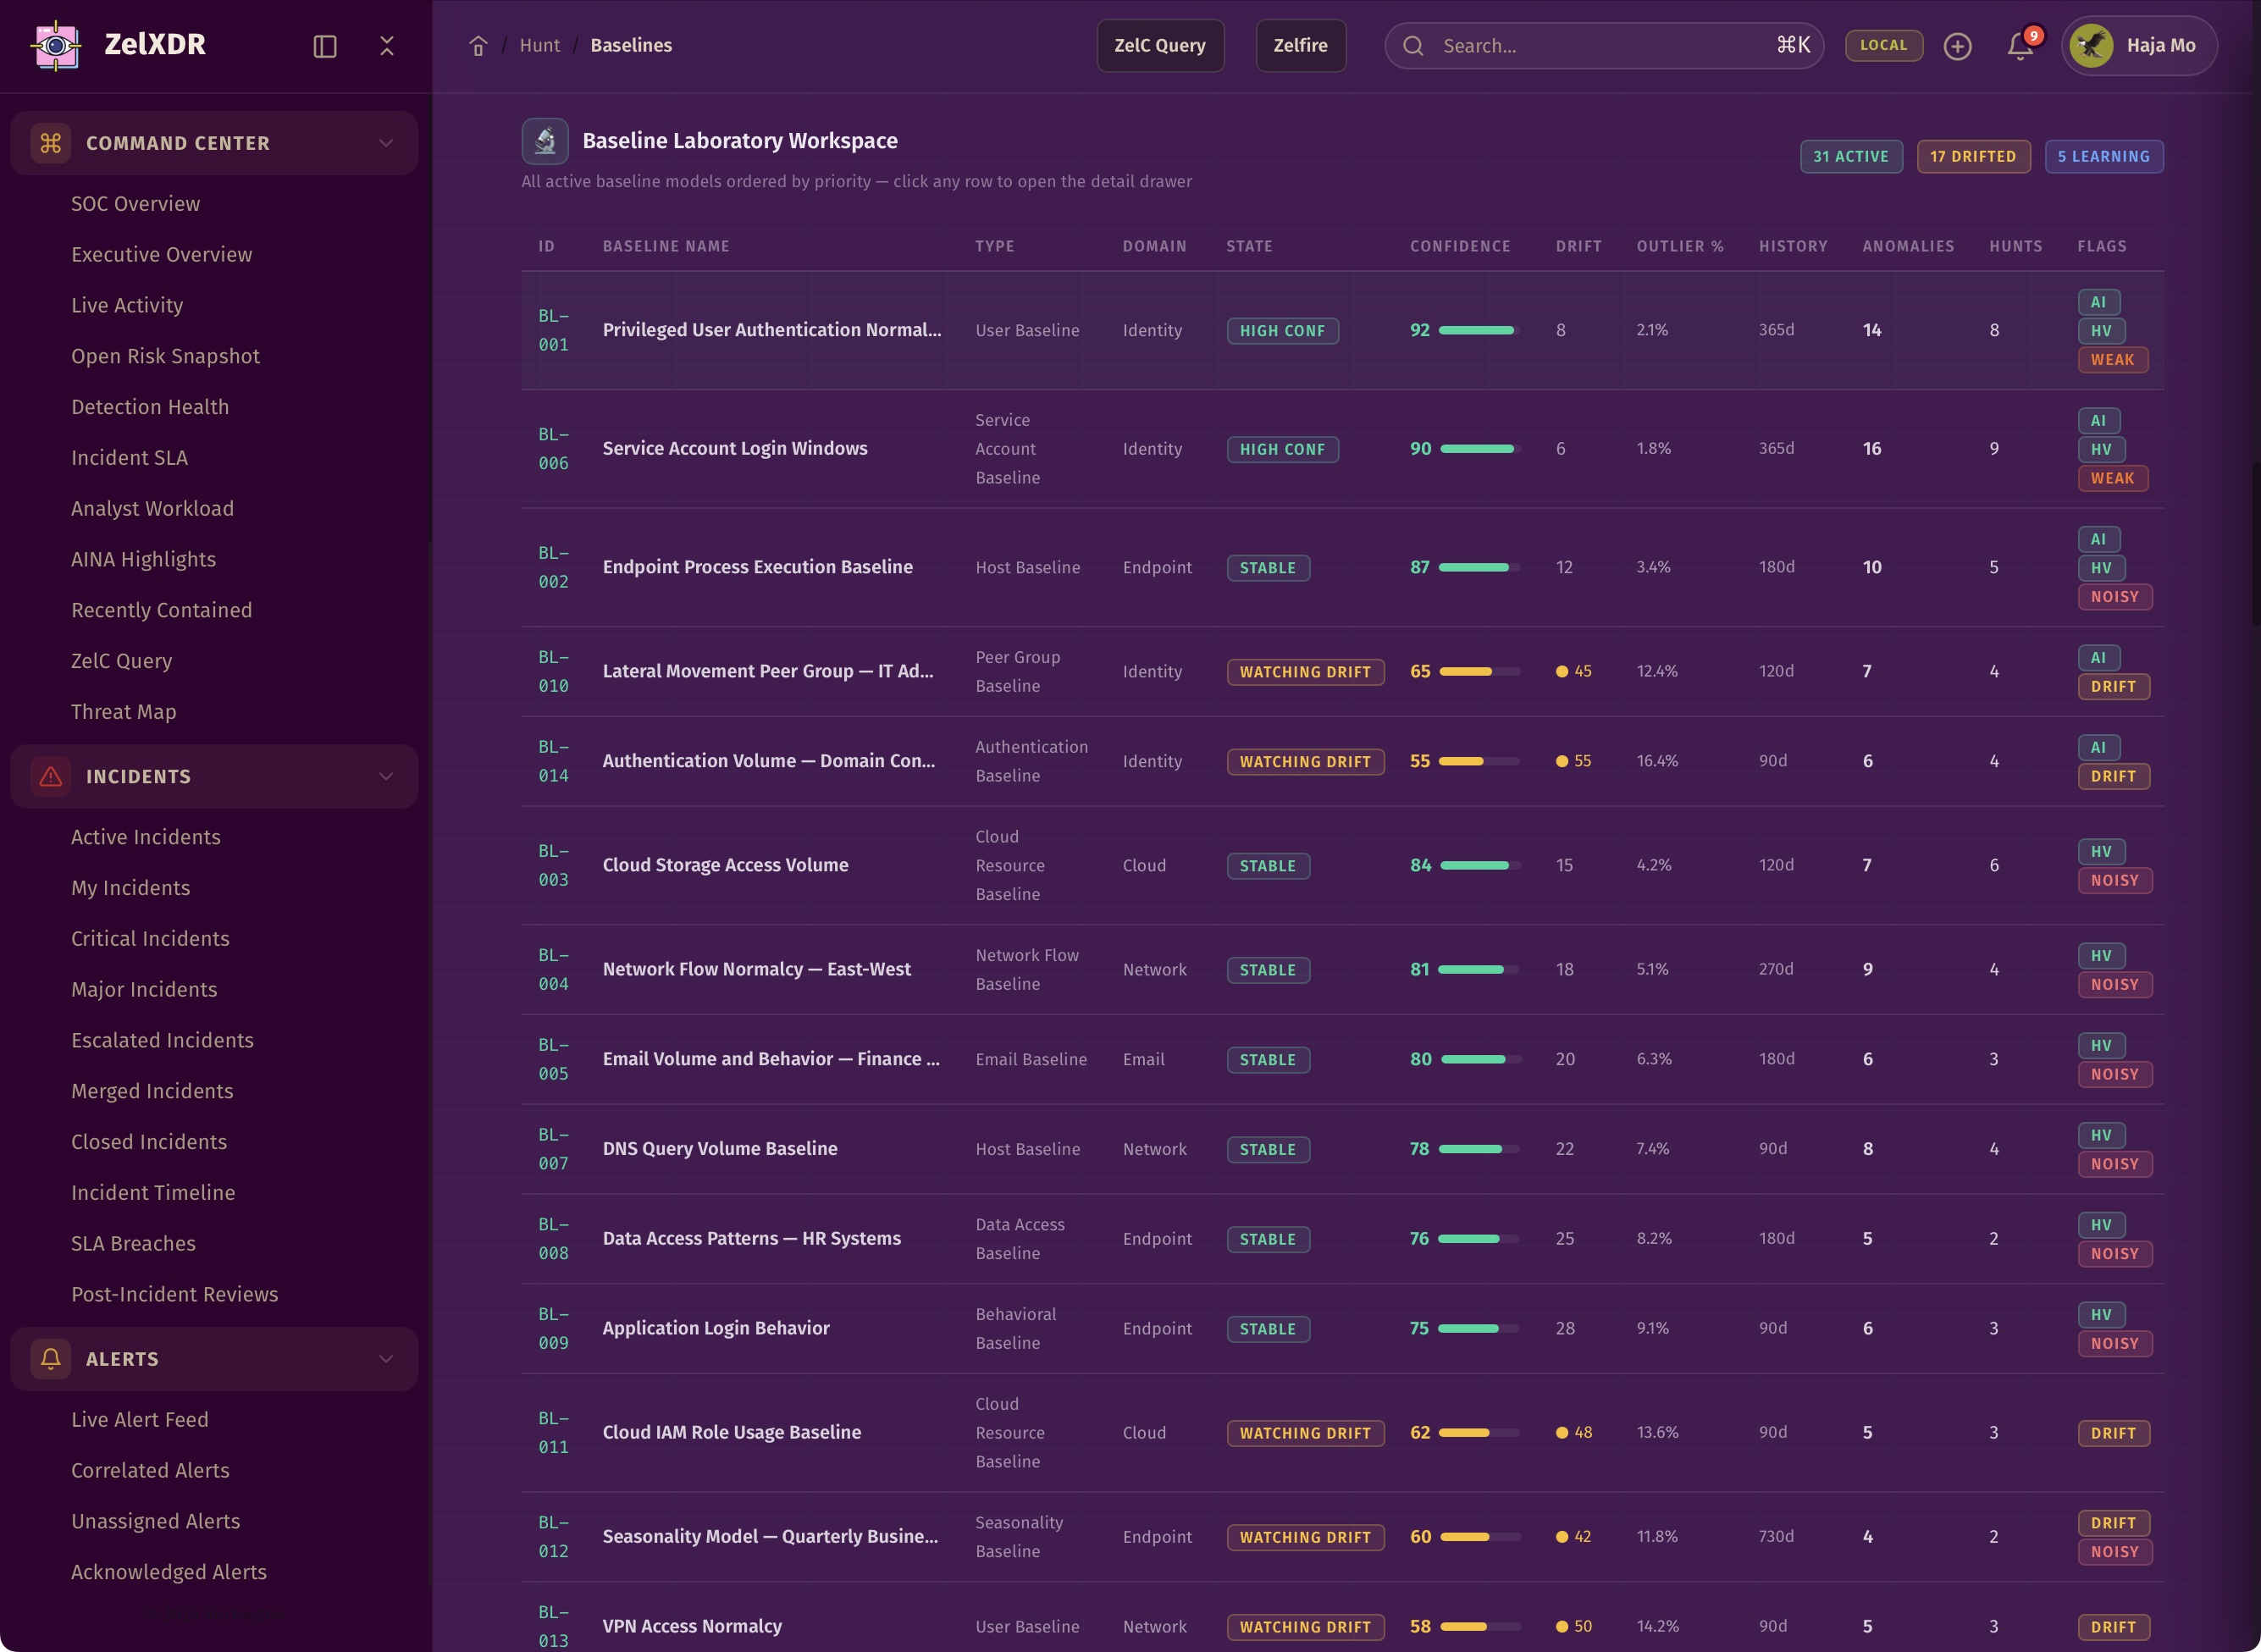
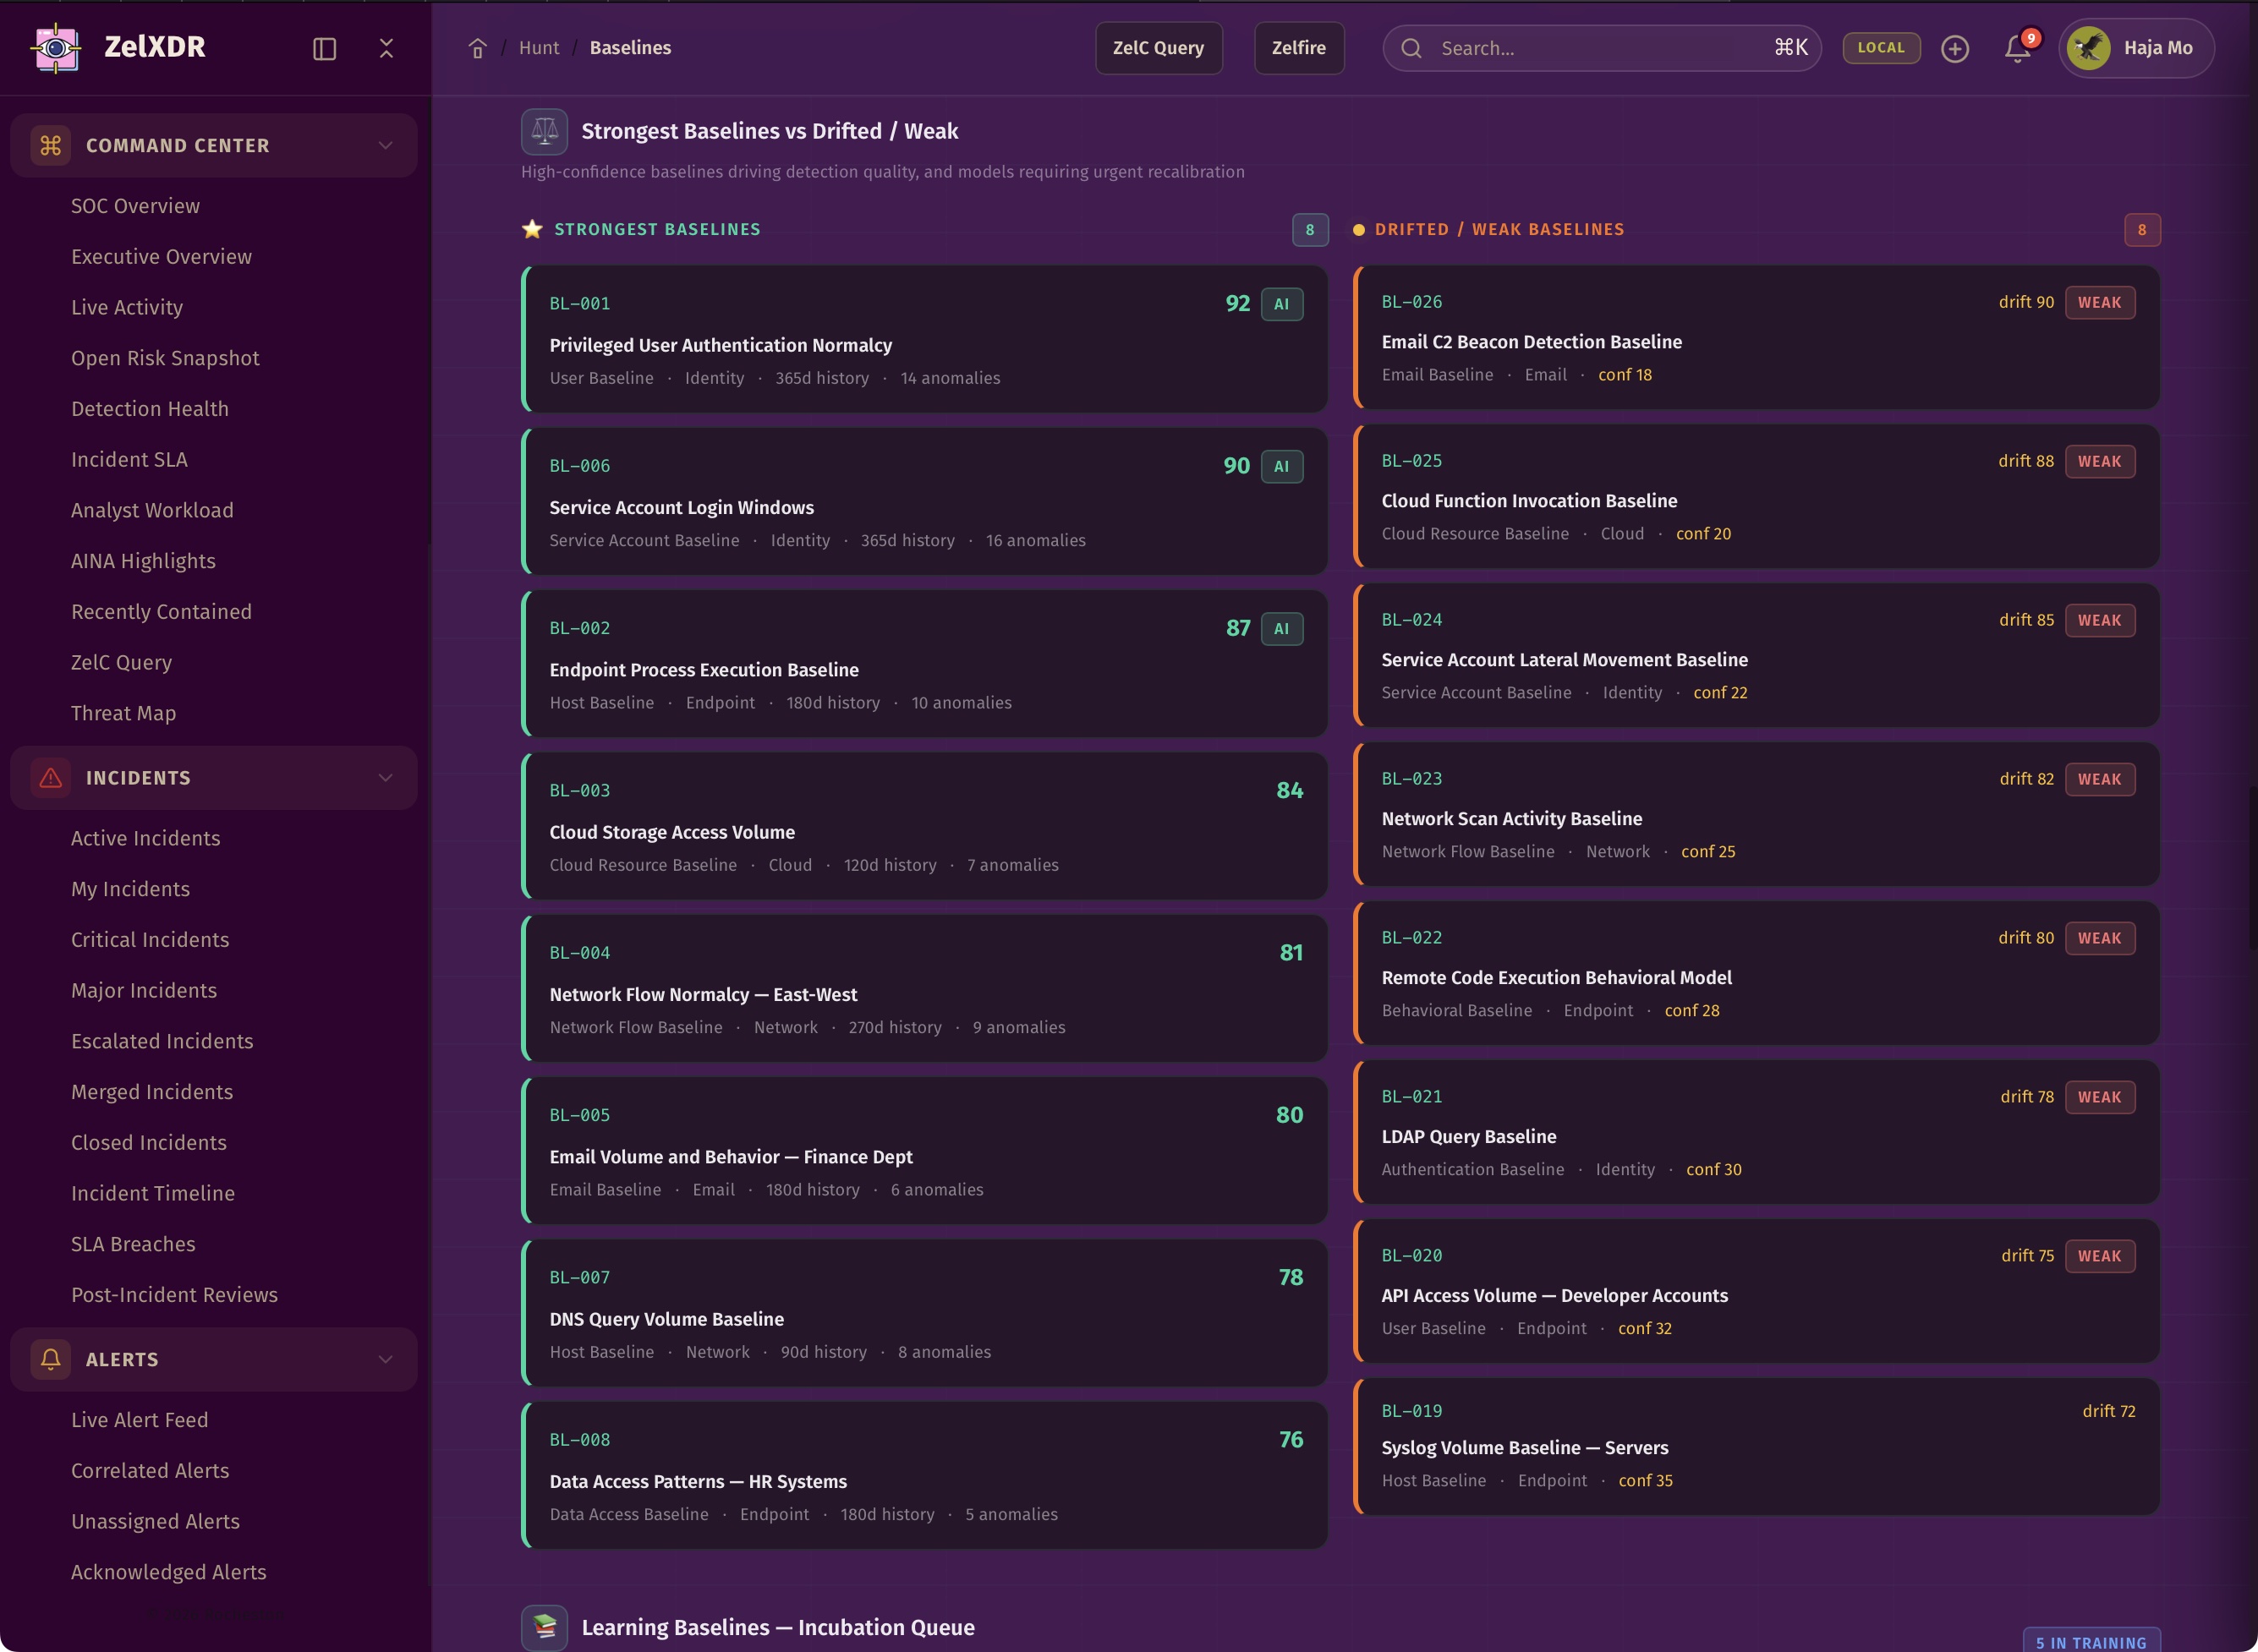
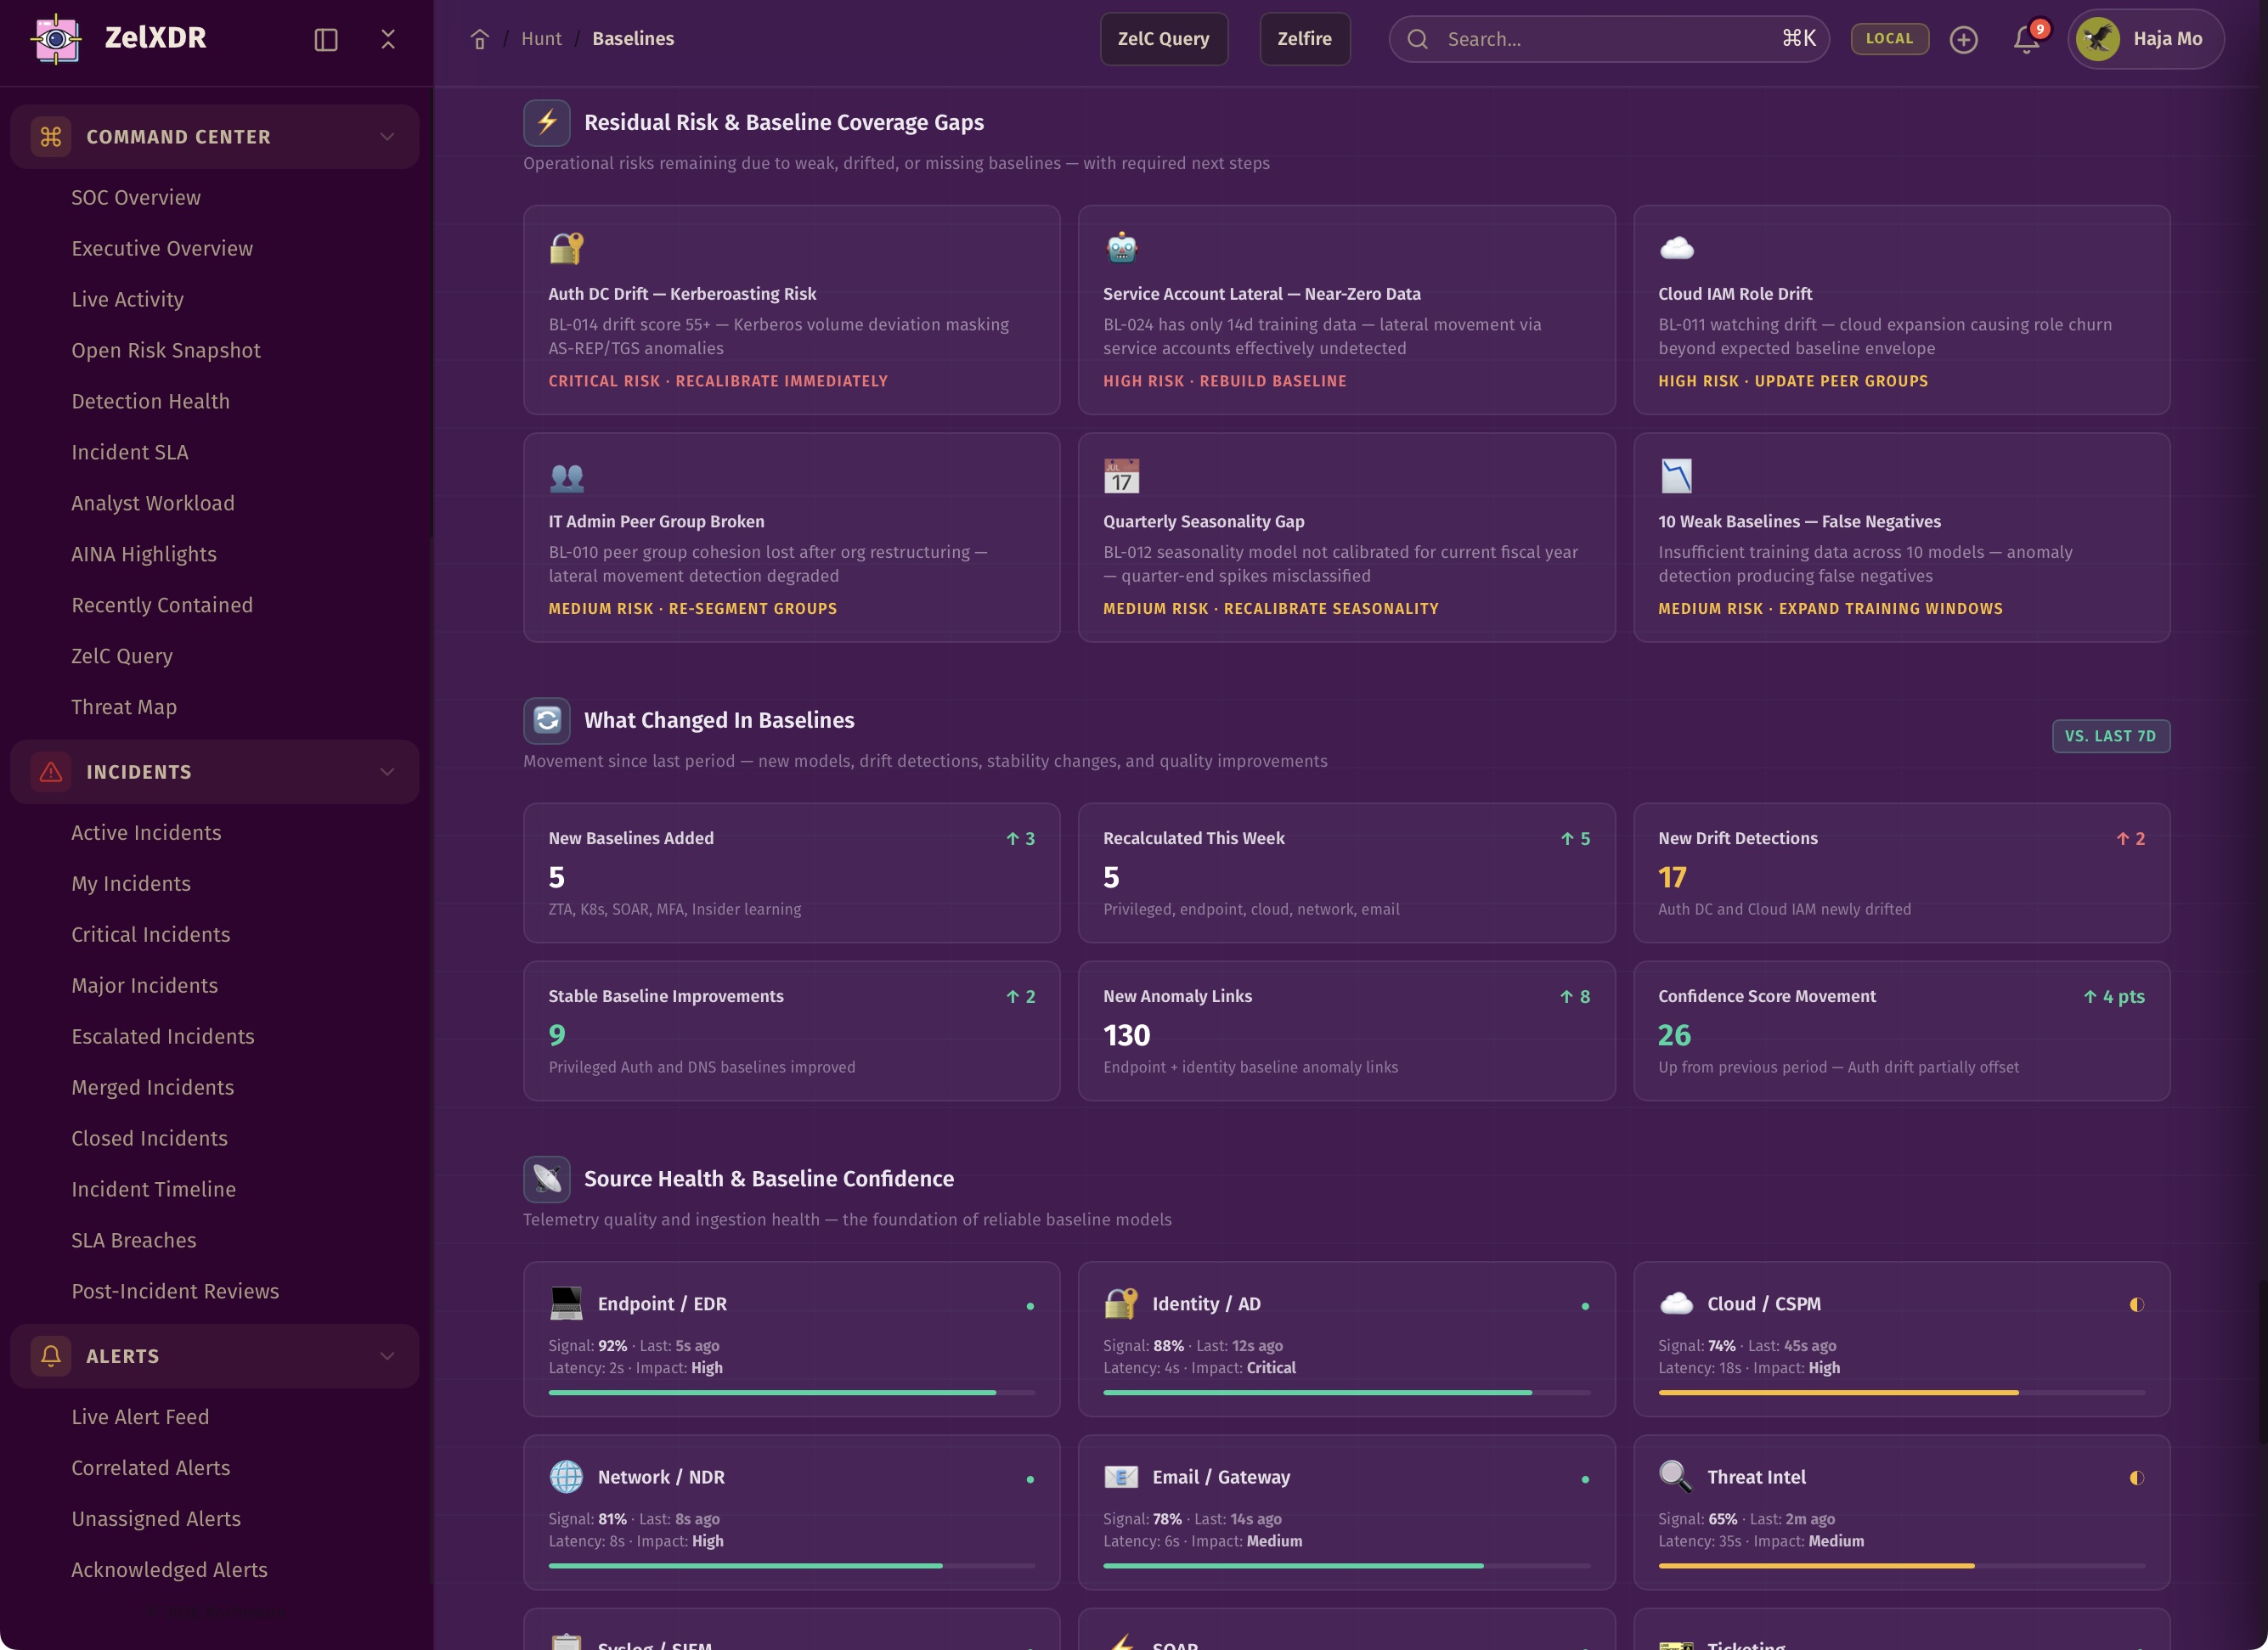
ZelXDR builds expected behavior models across users, hosts, cloud resources, services, and peer groups. This helps teams spot meaningful deviations instead of chasing every unusual signal.
You find real anomalies only when you understand normal.
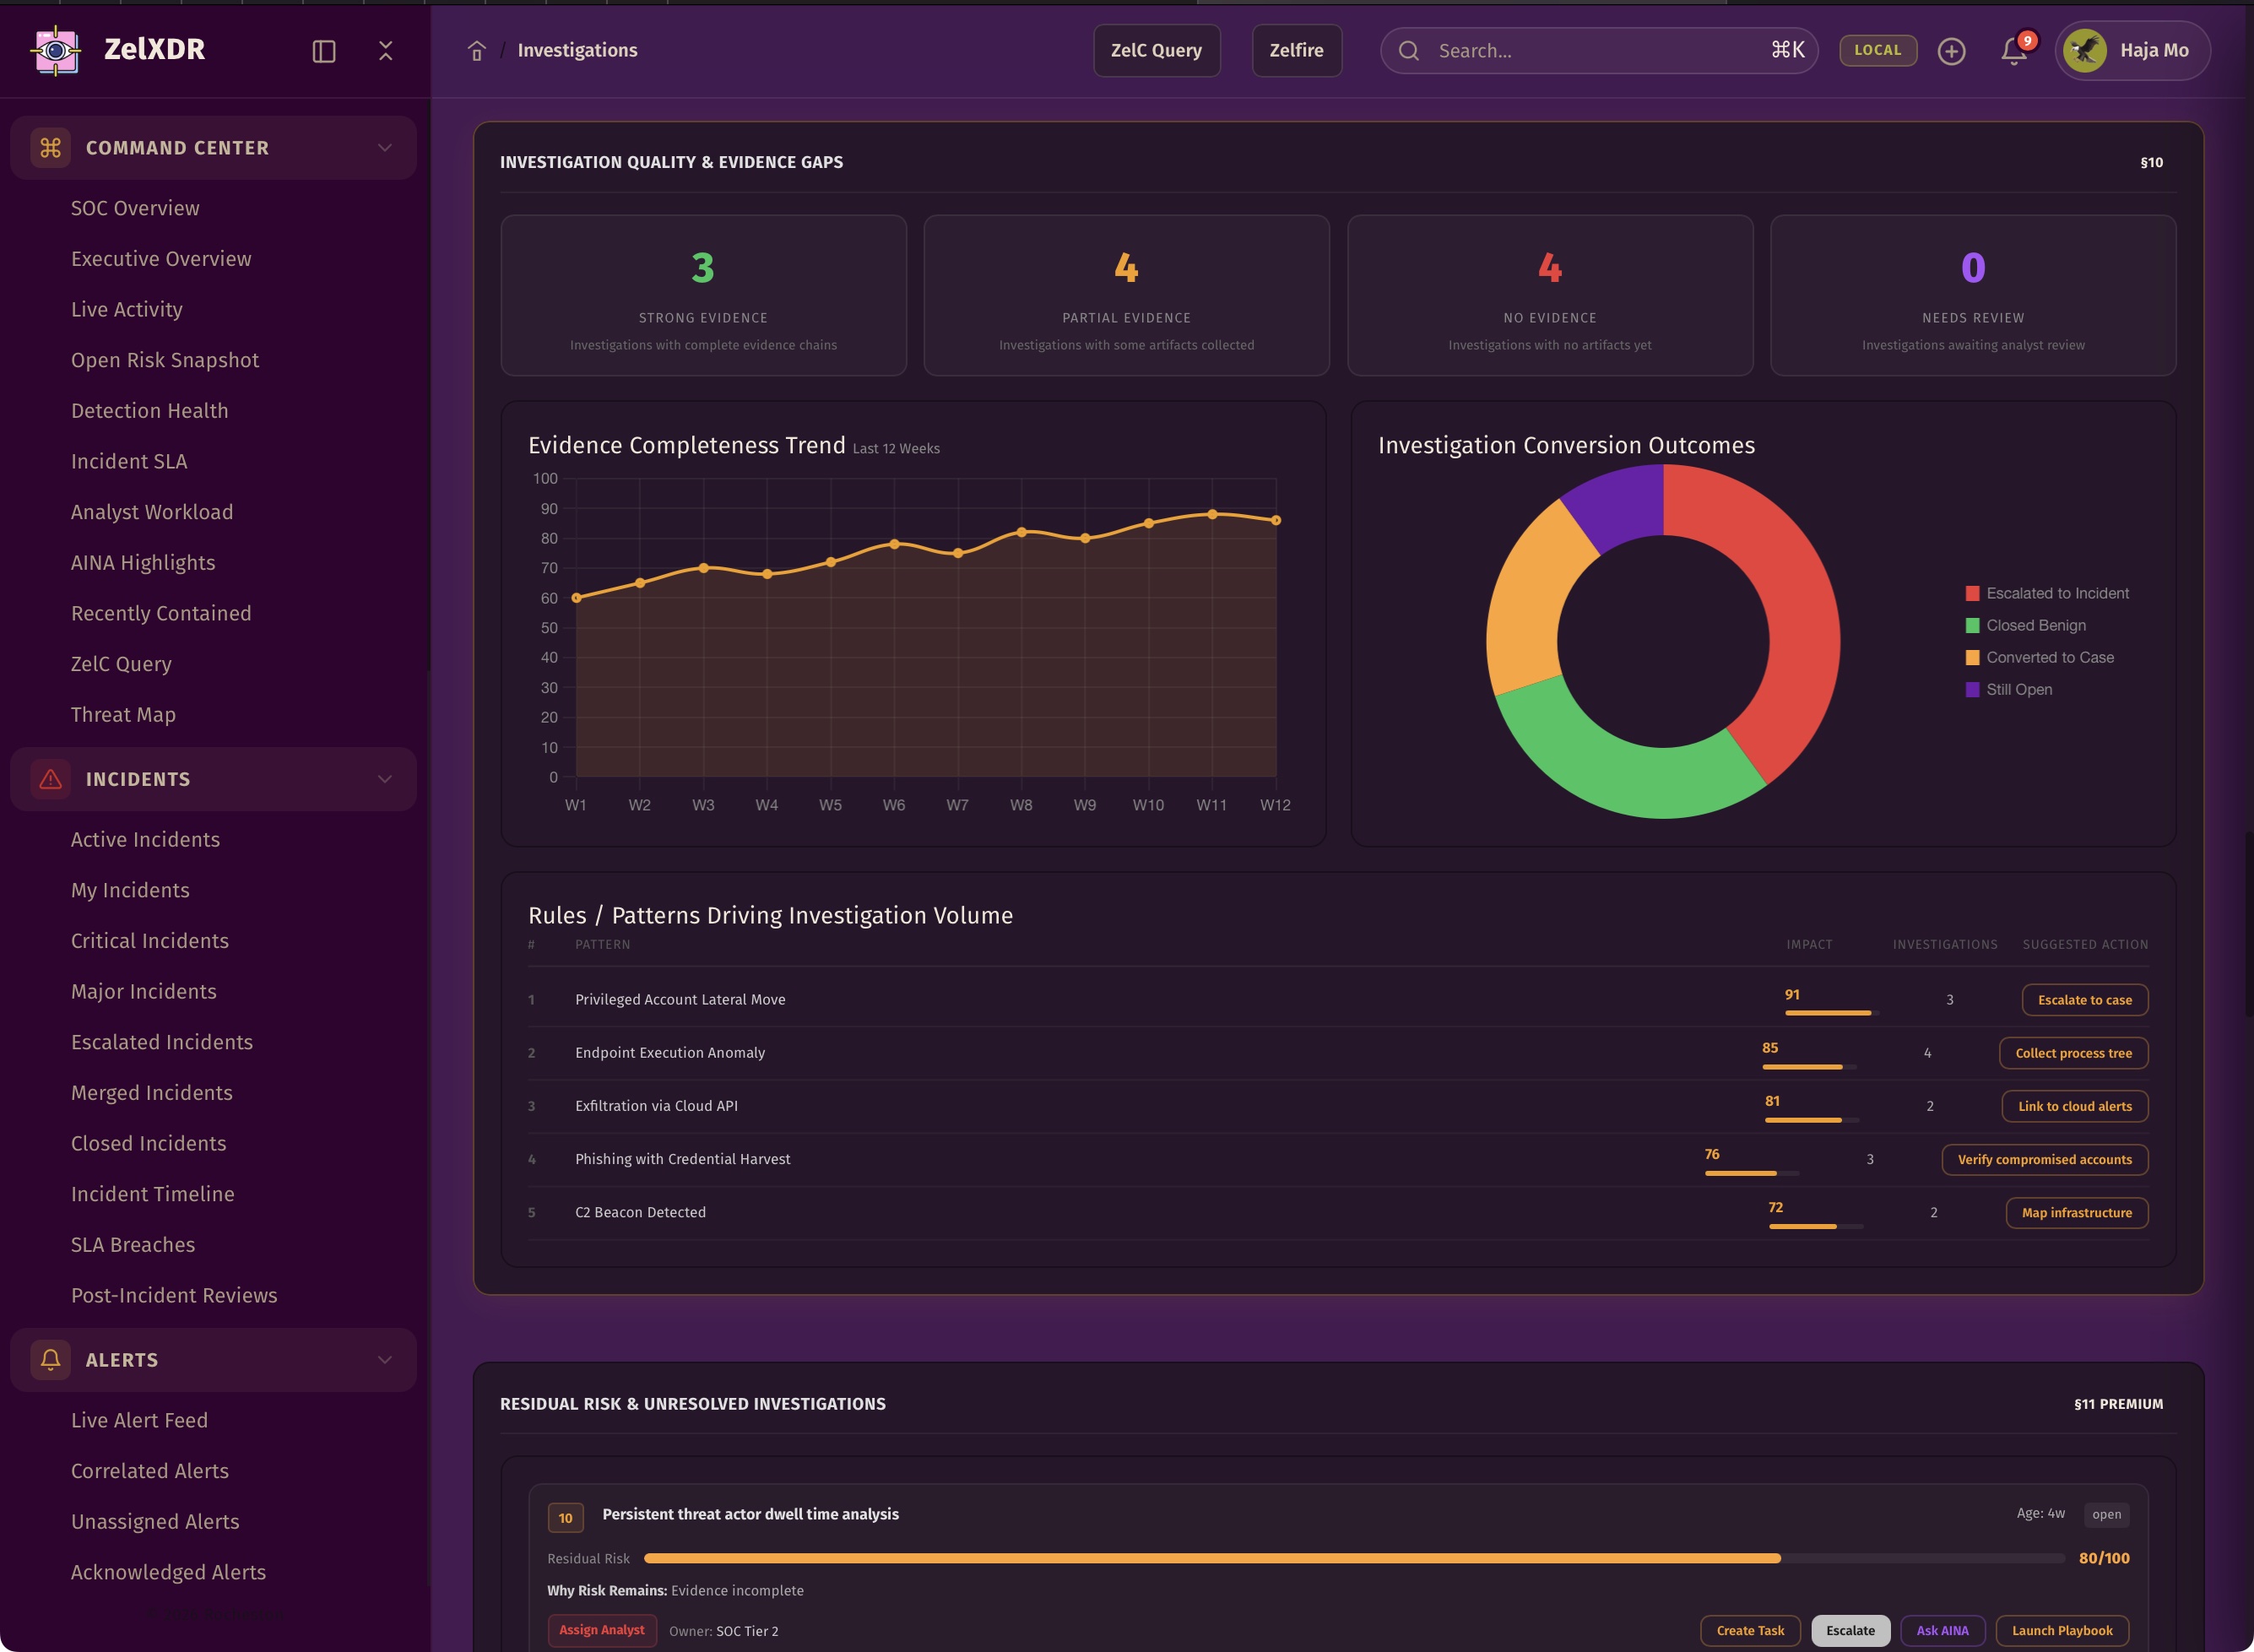
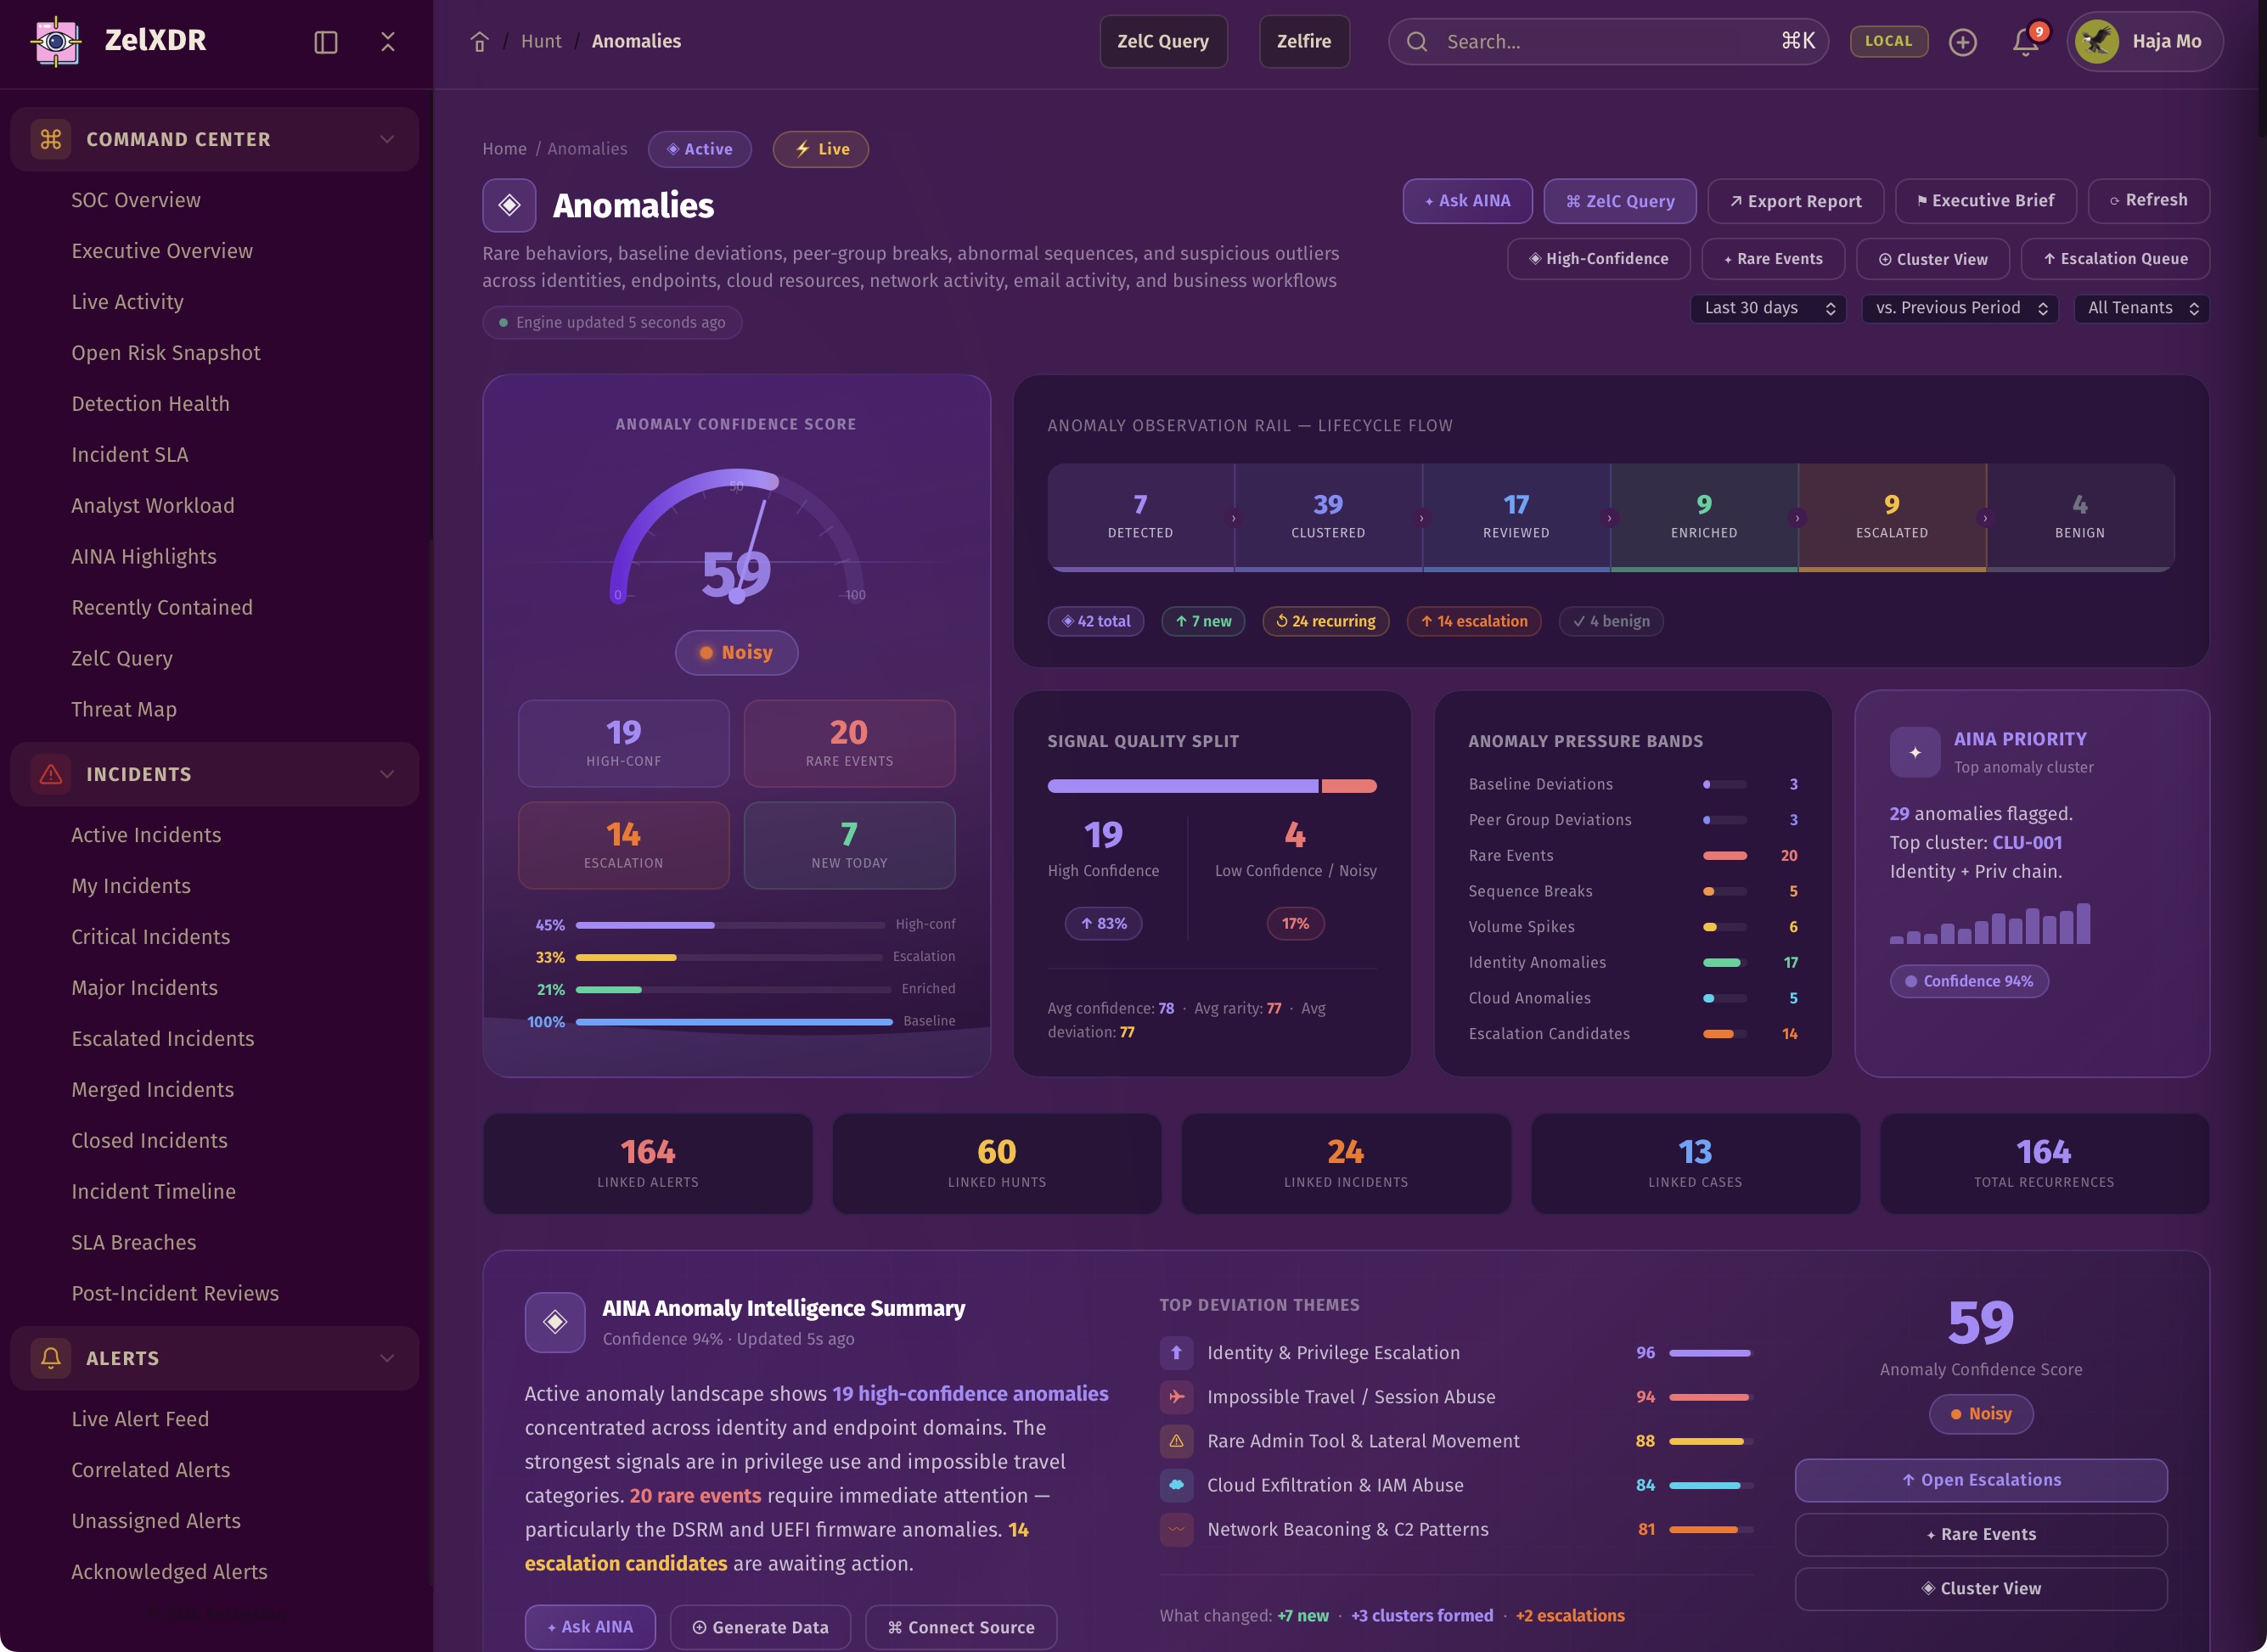
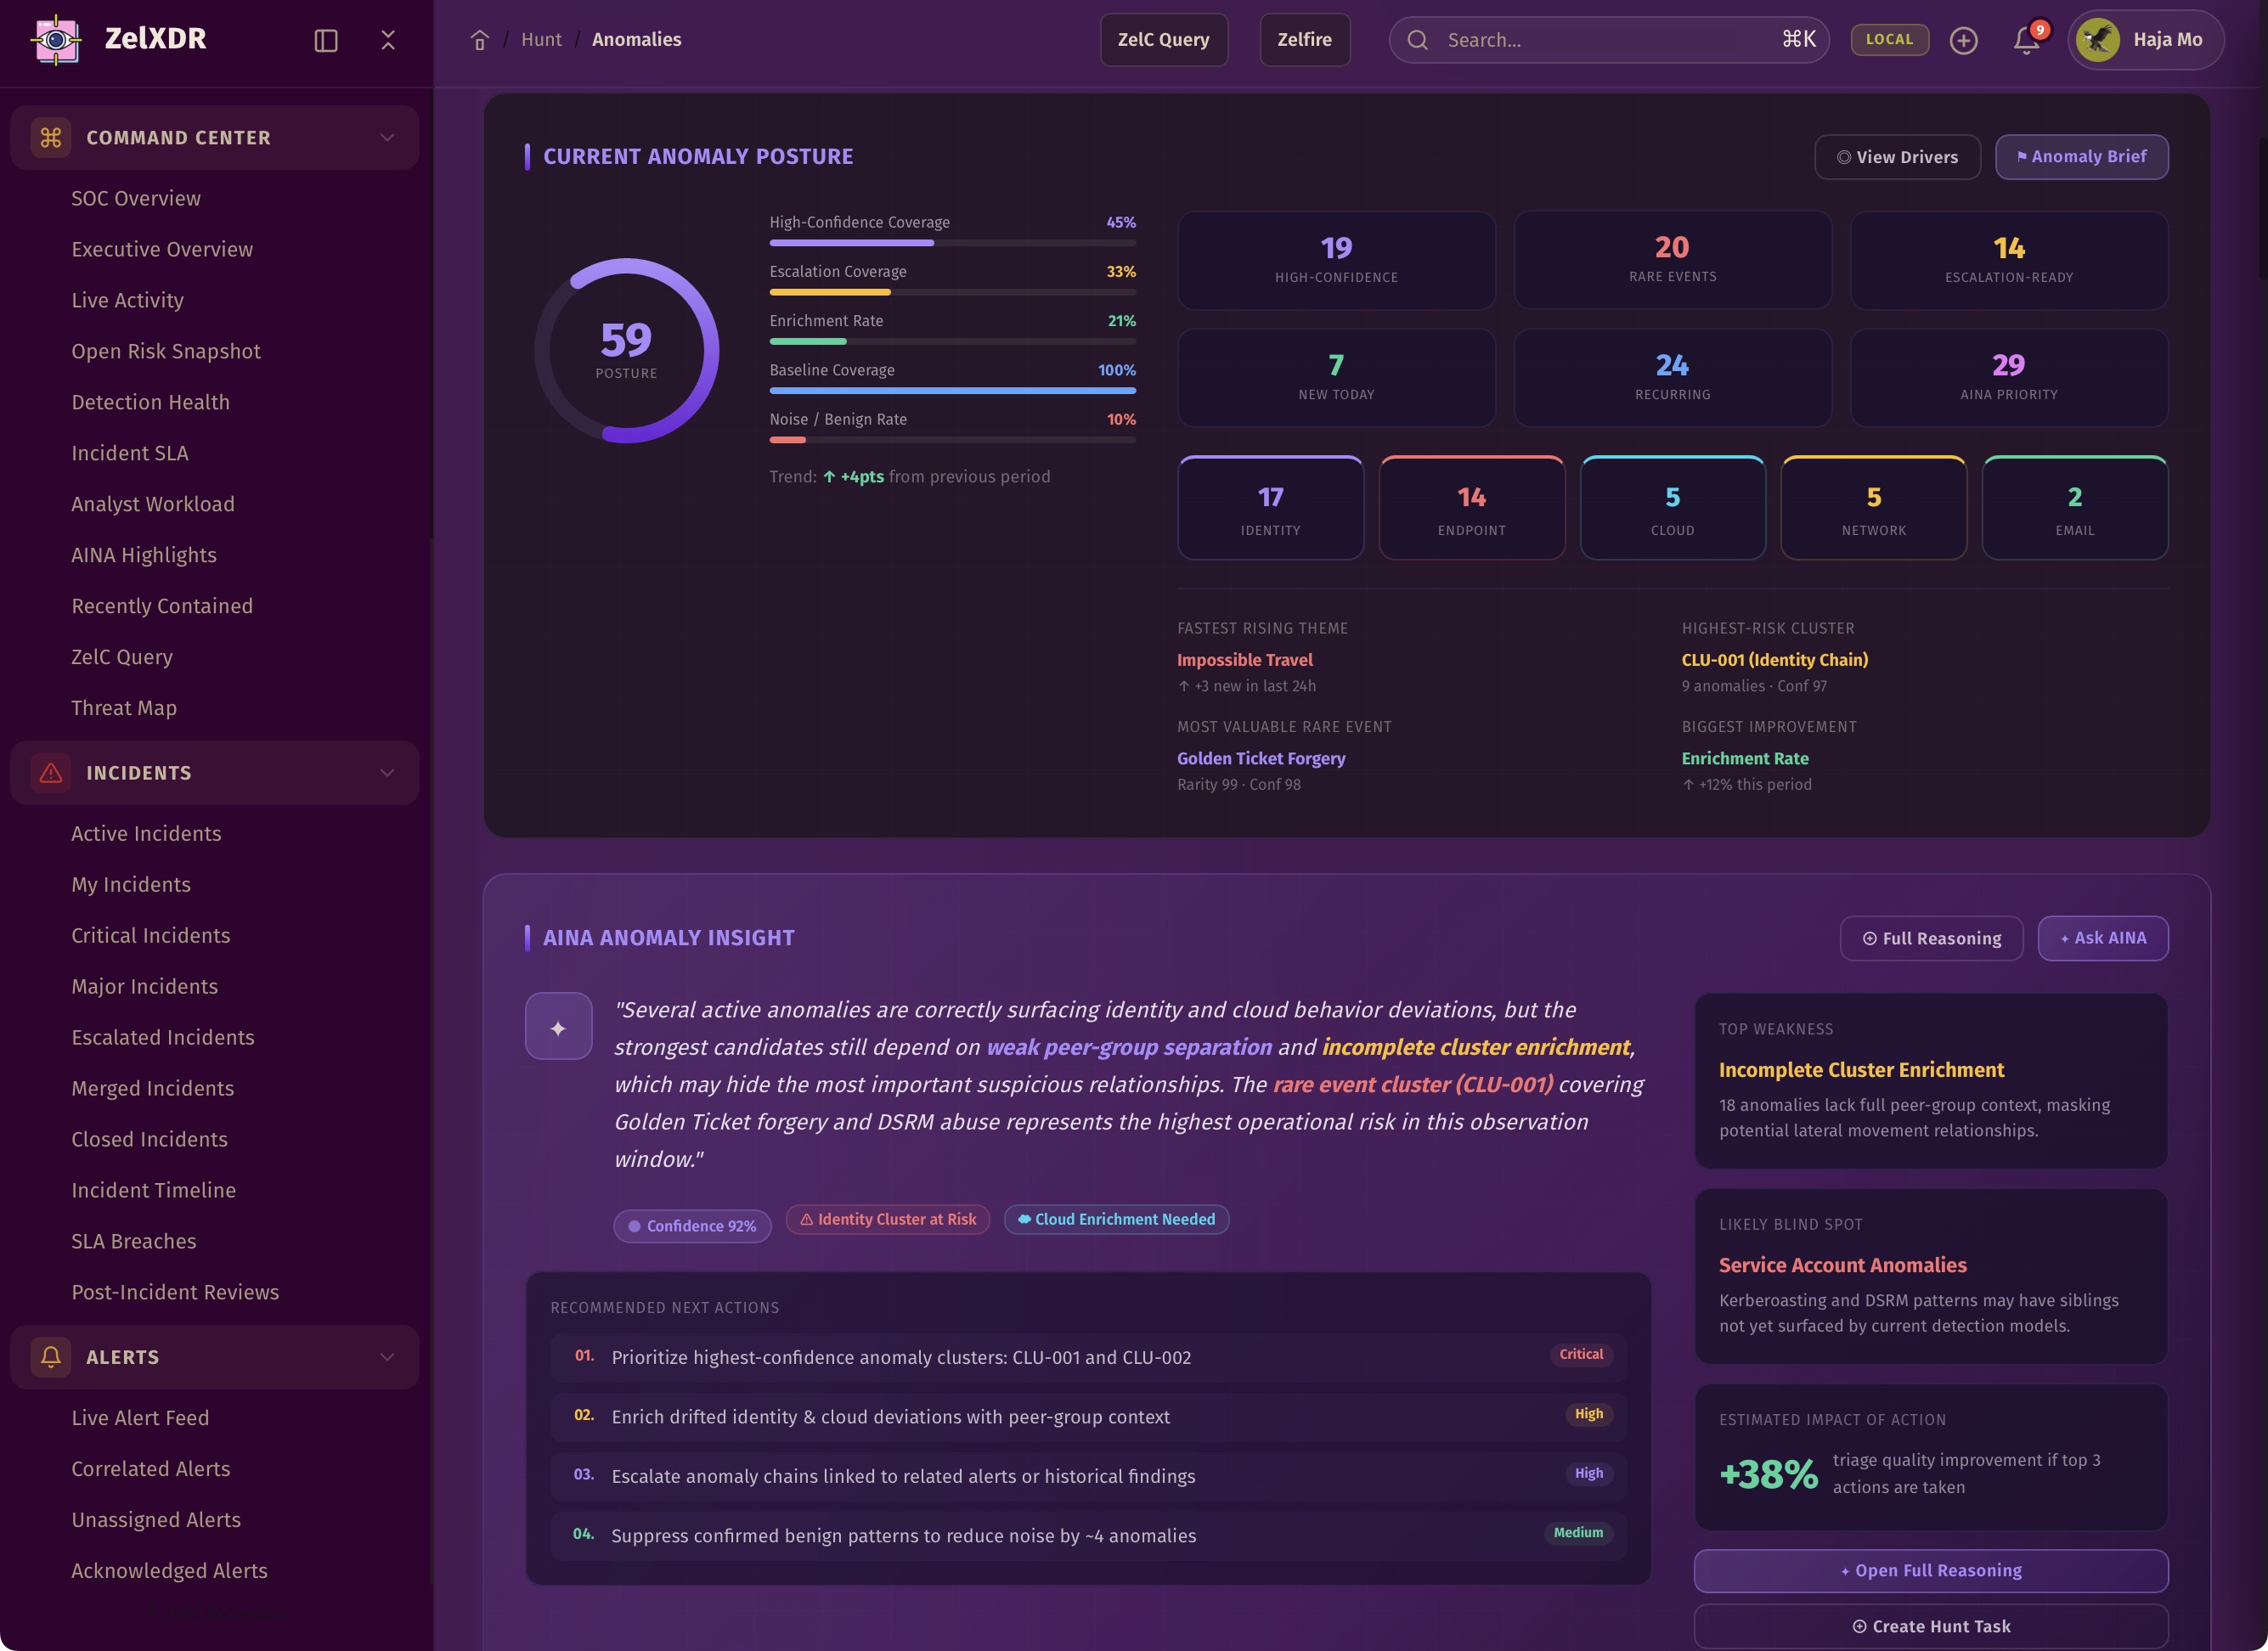
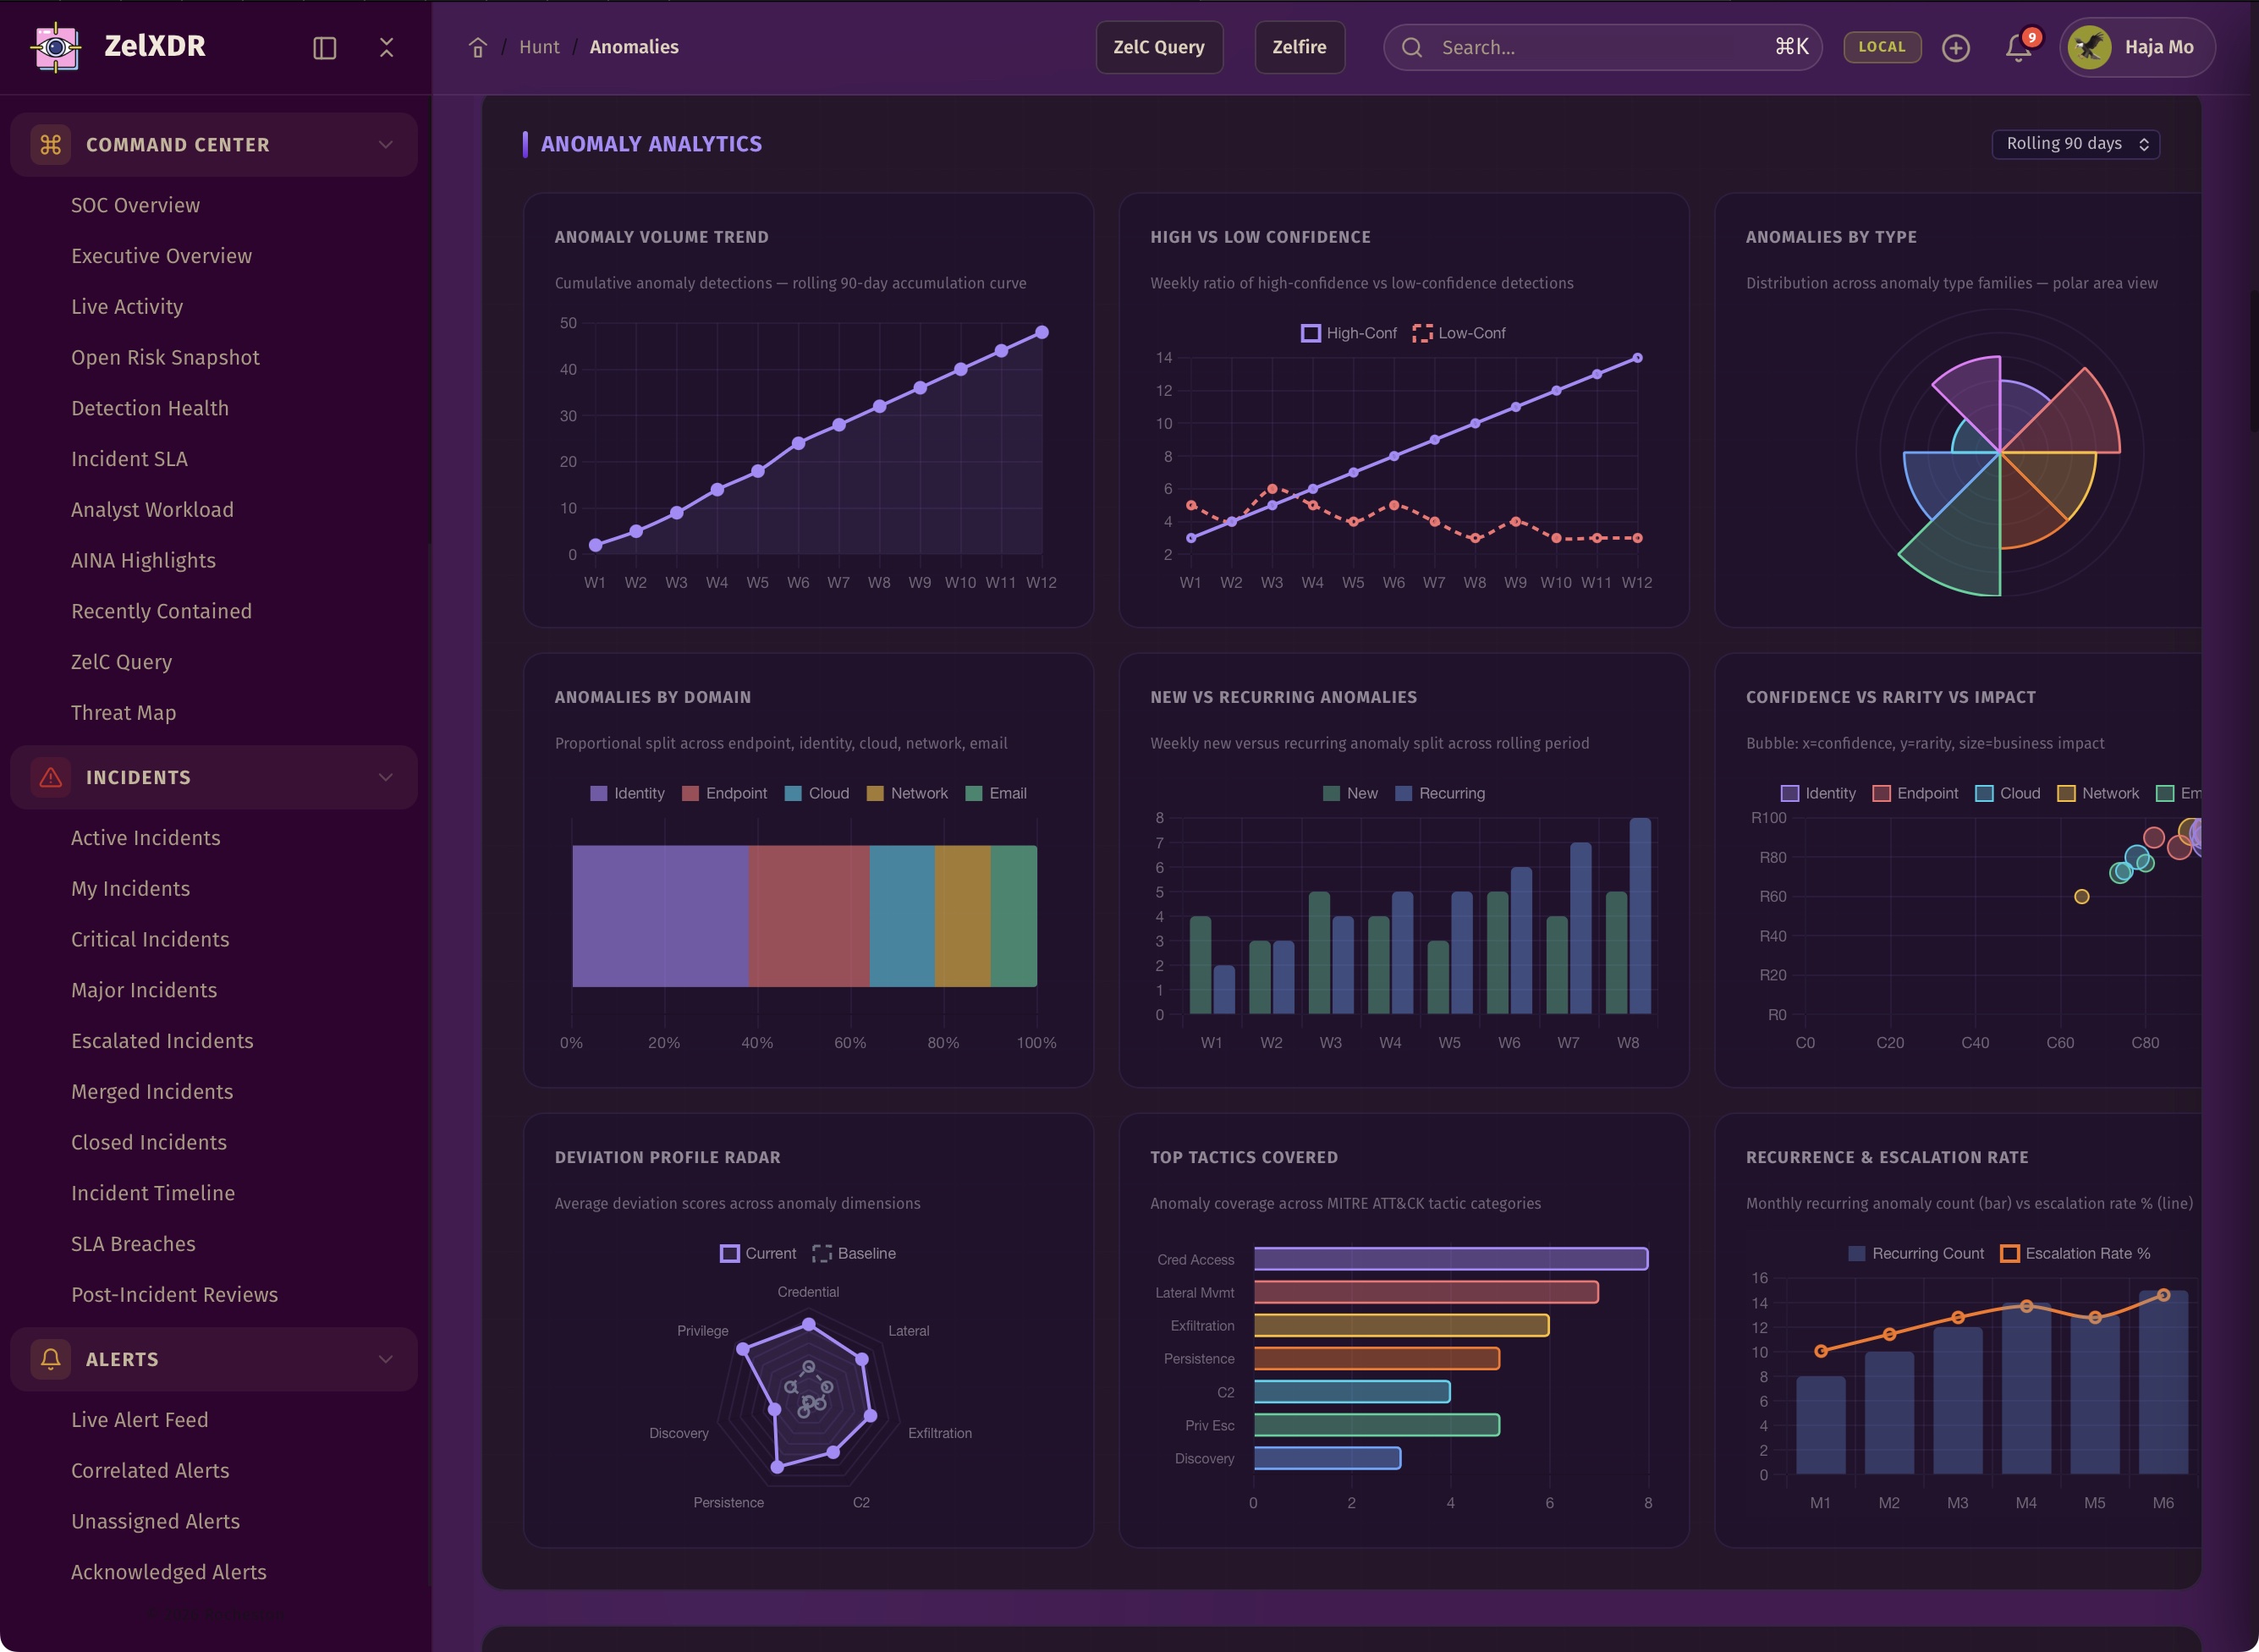
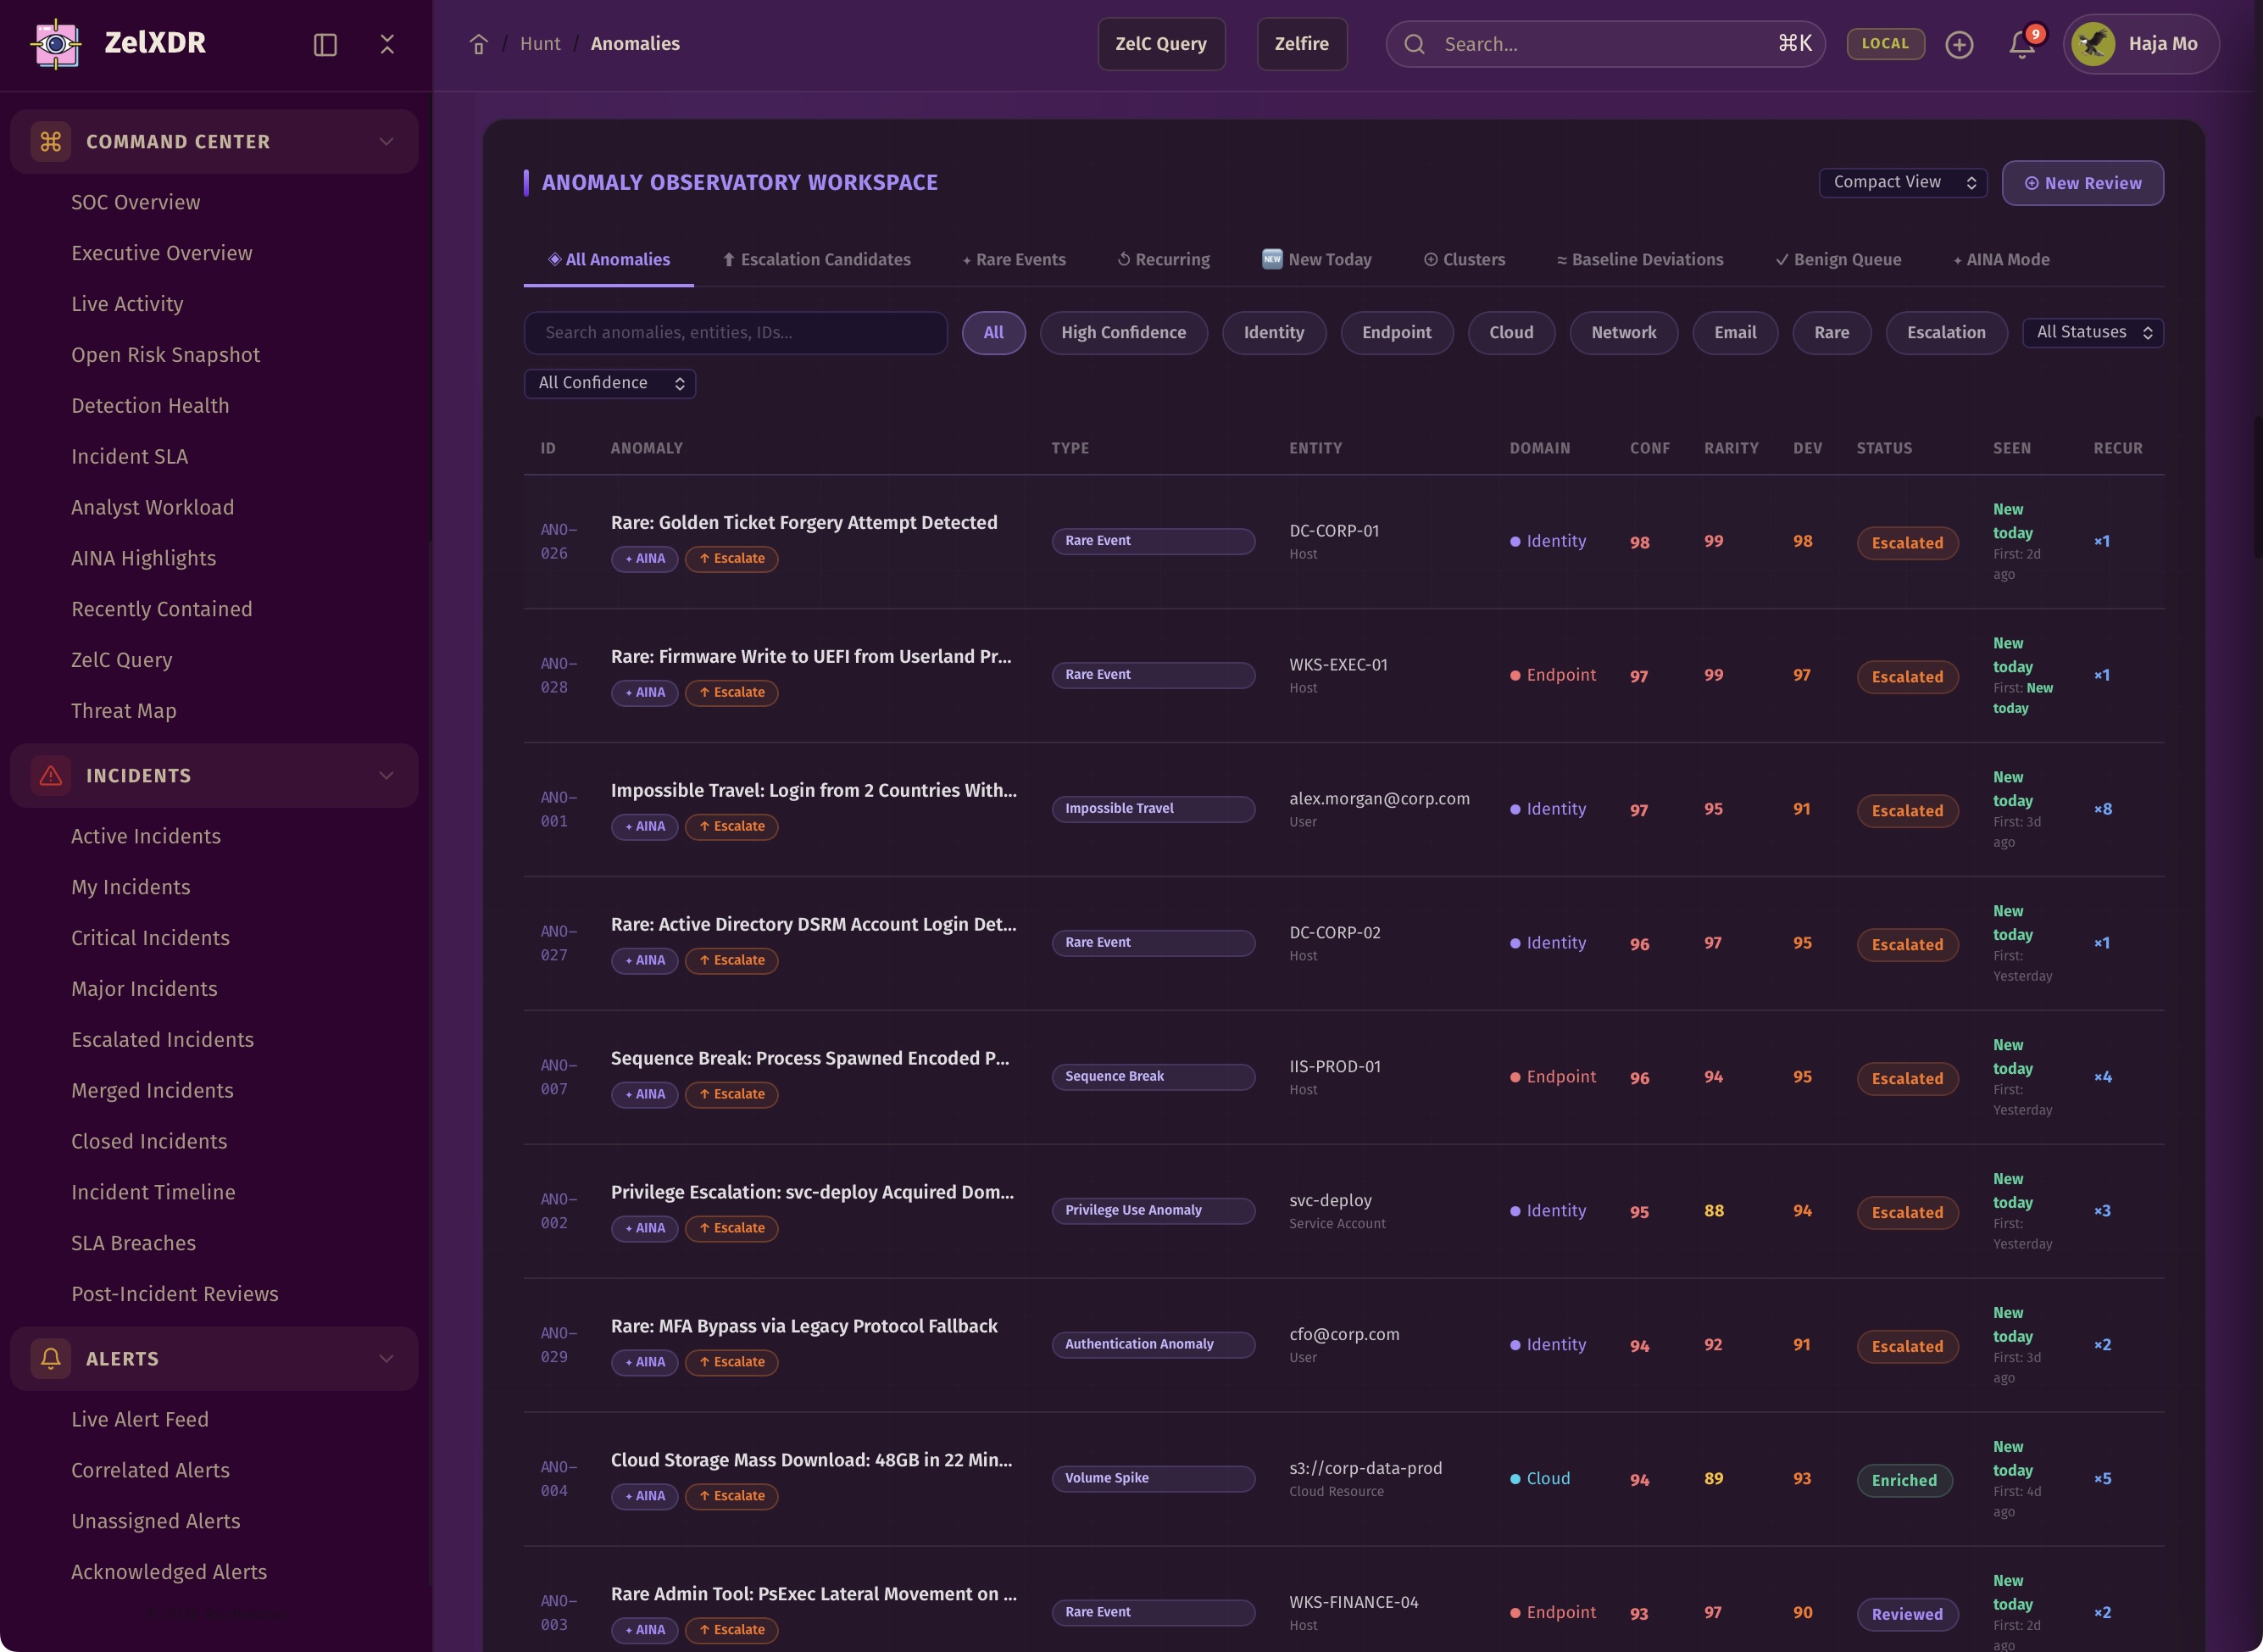
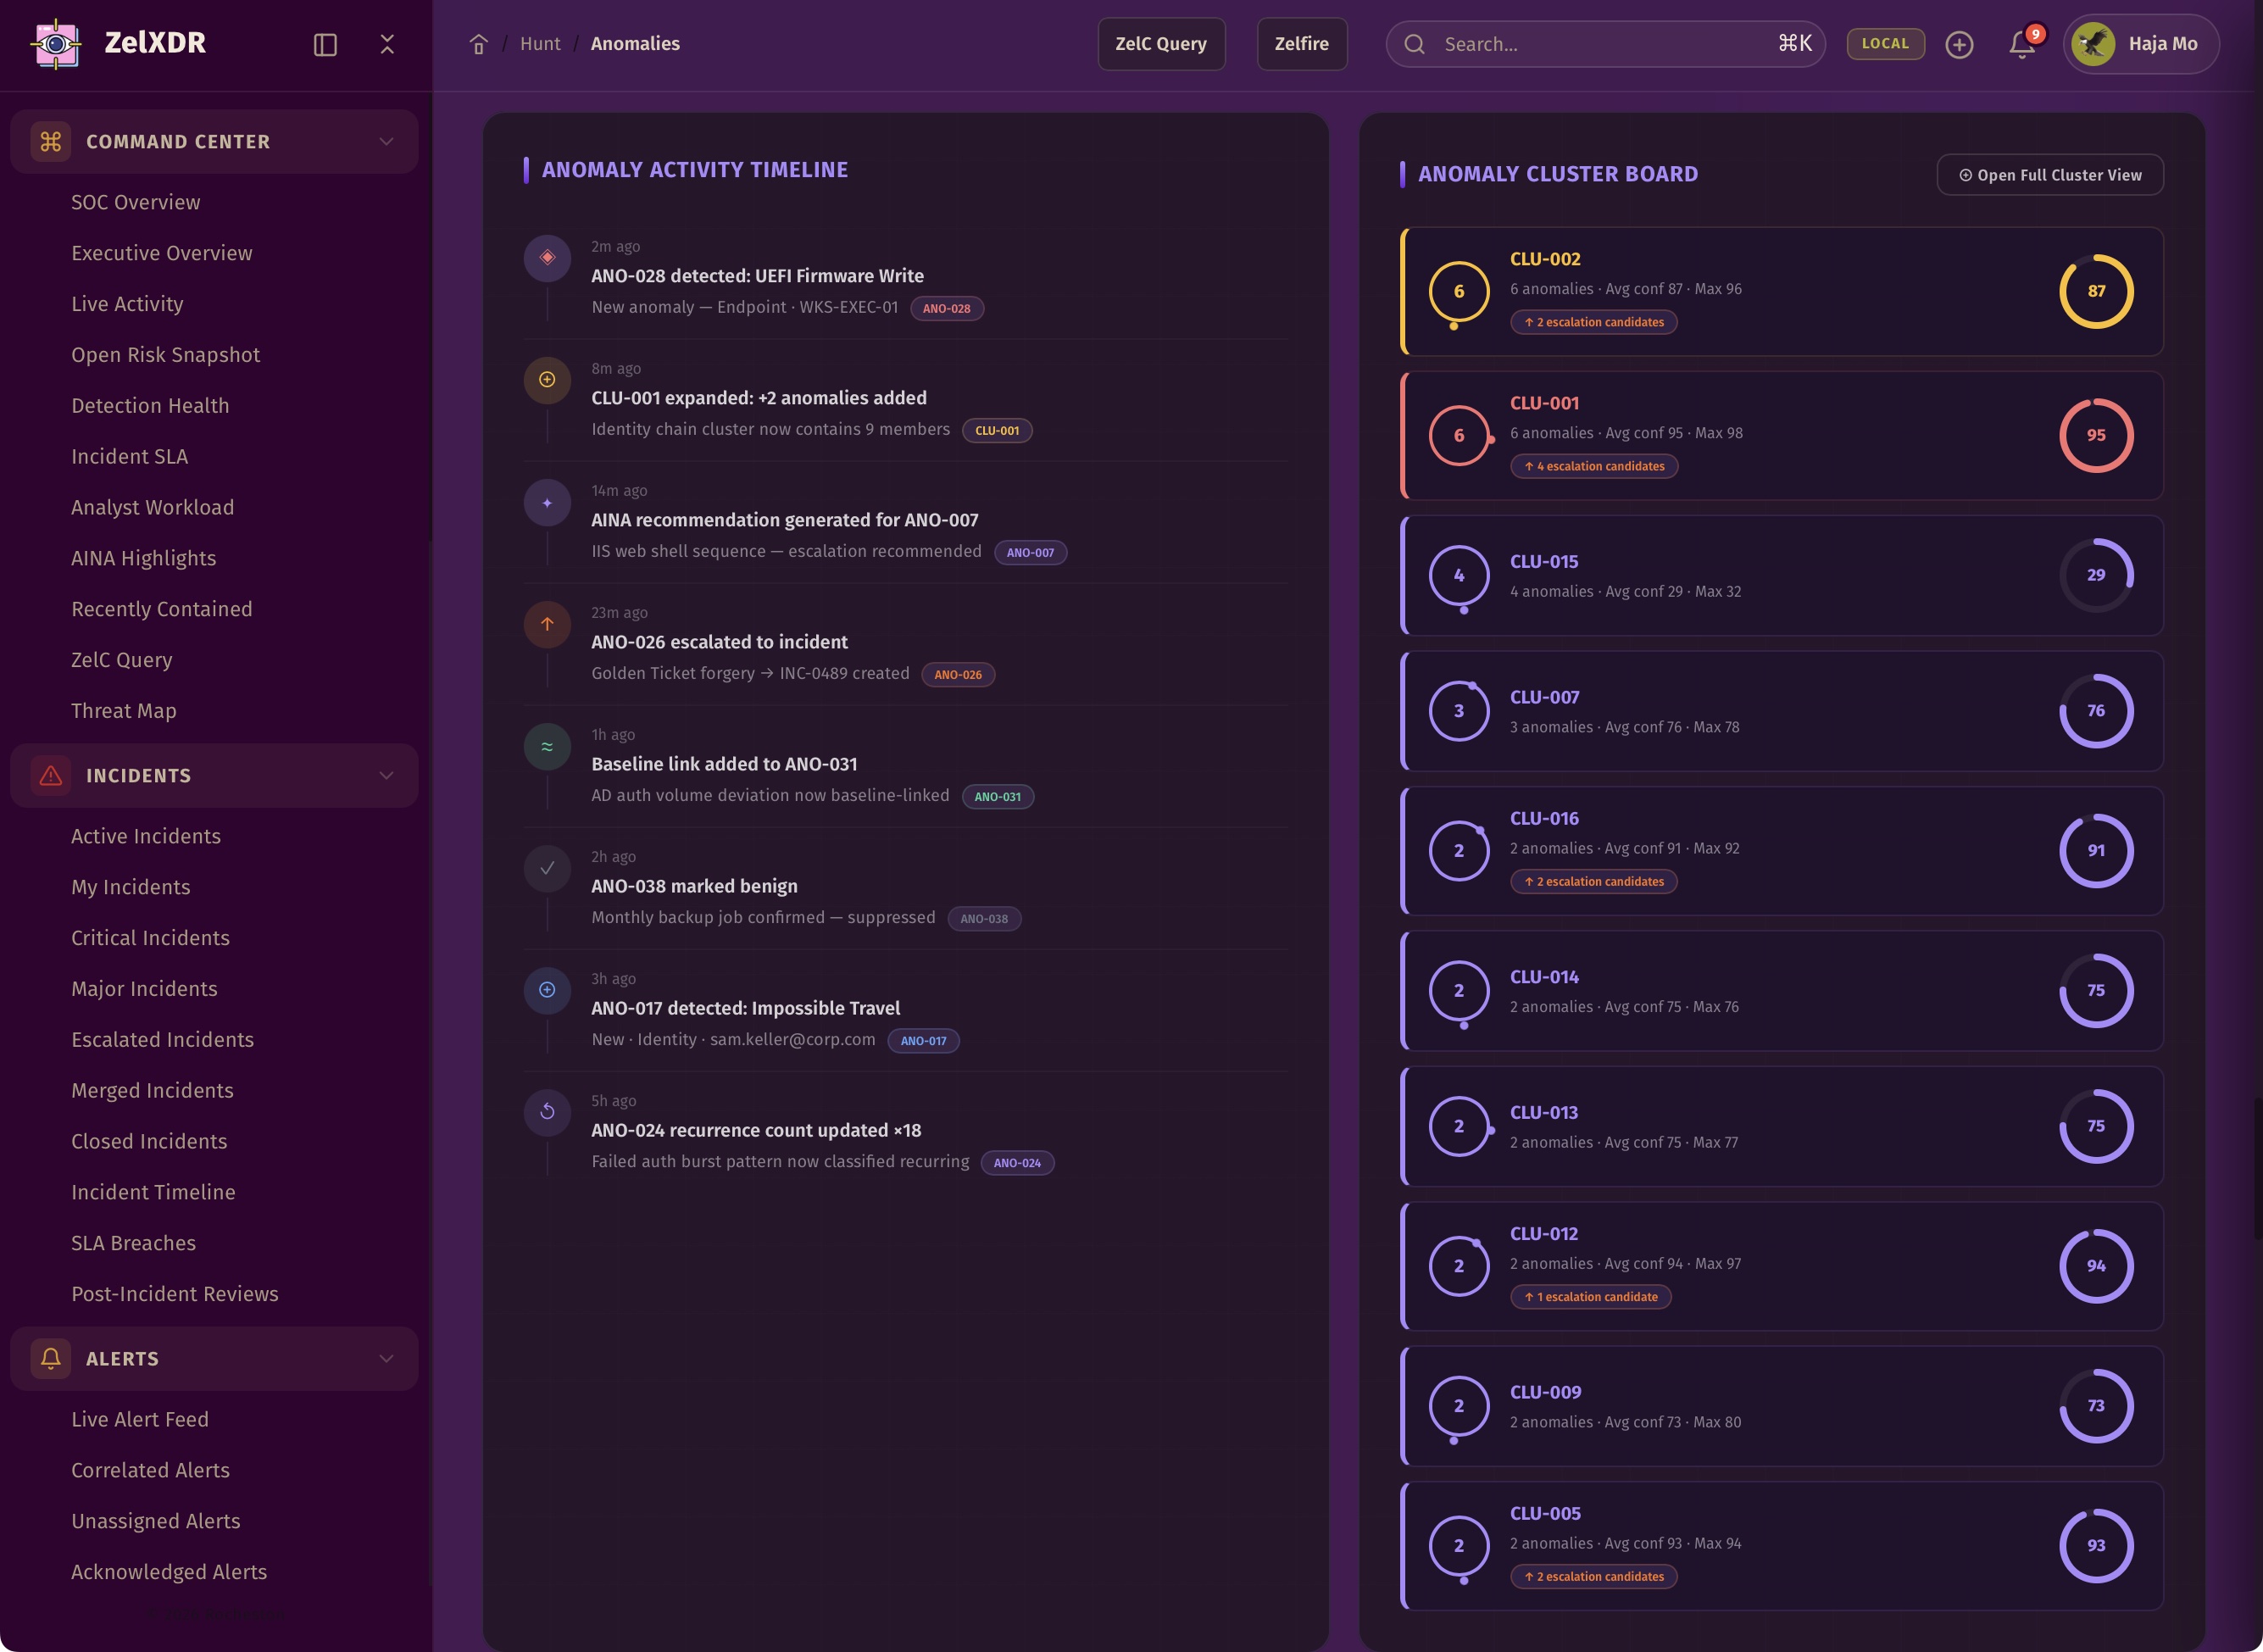
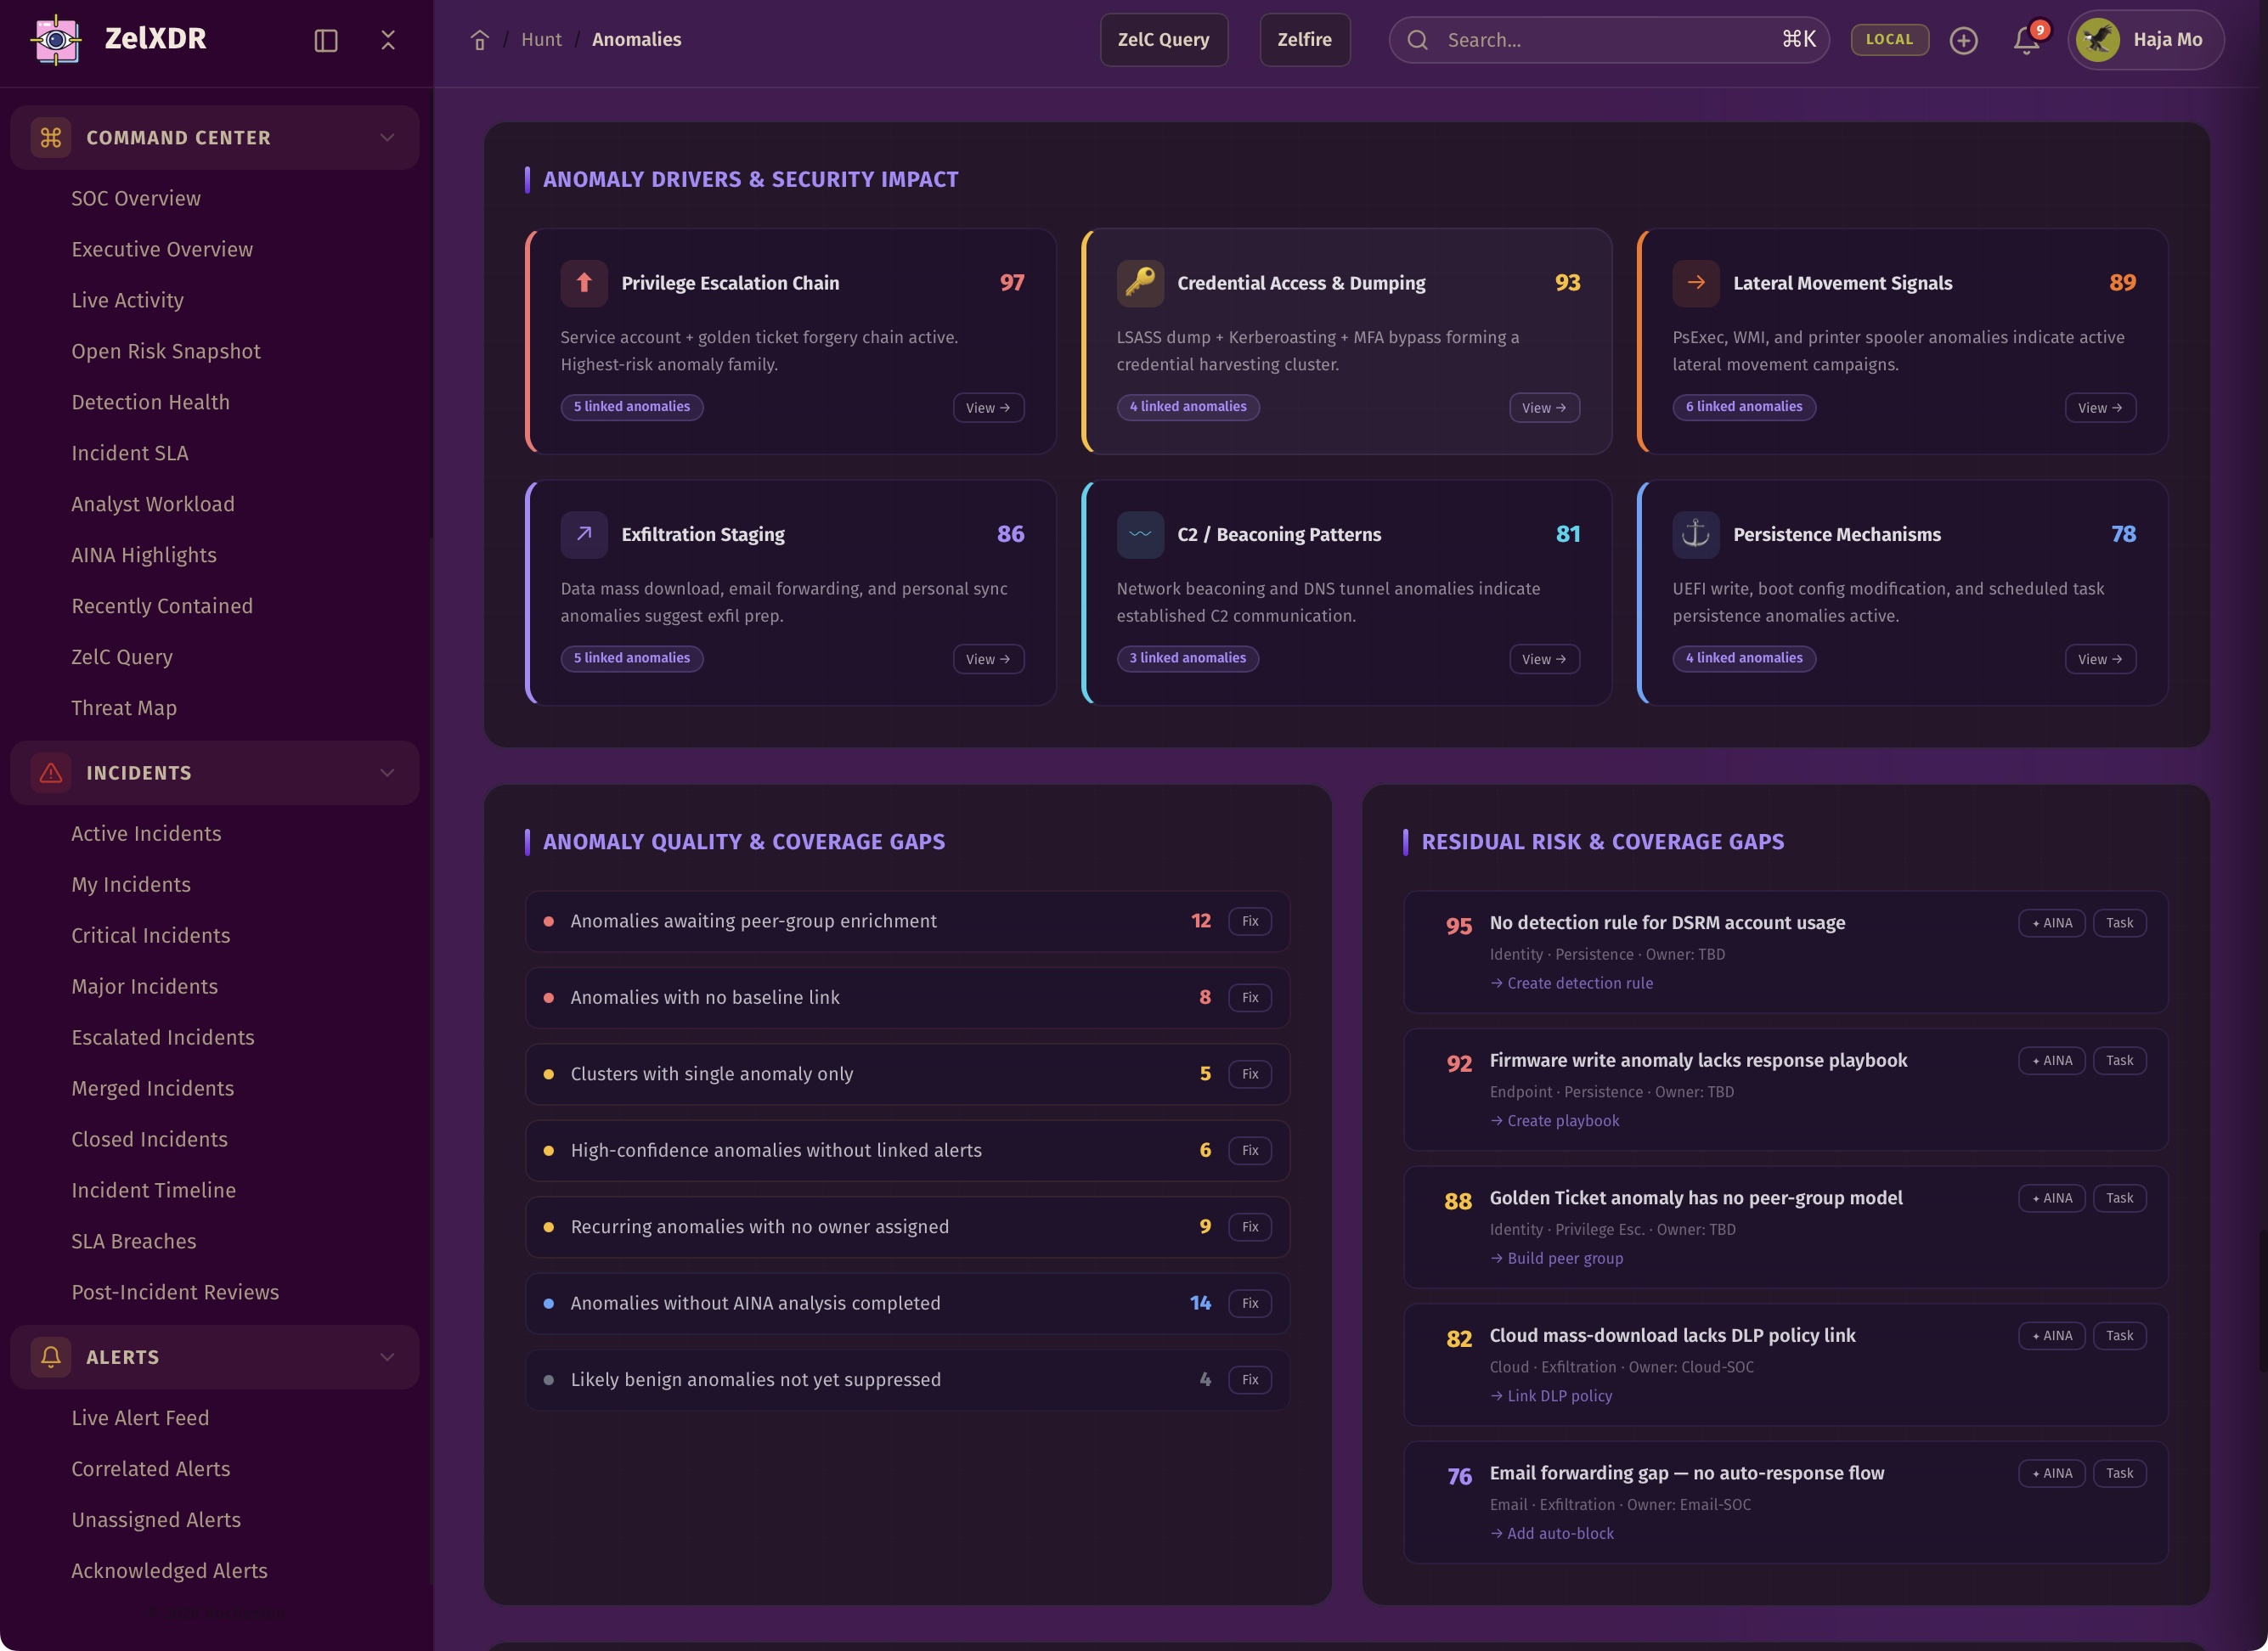
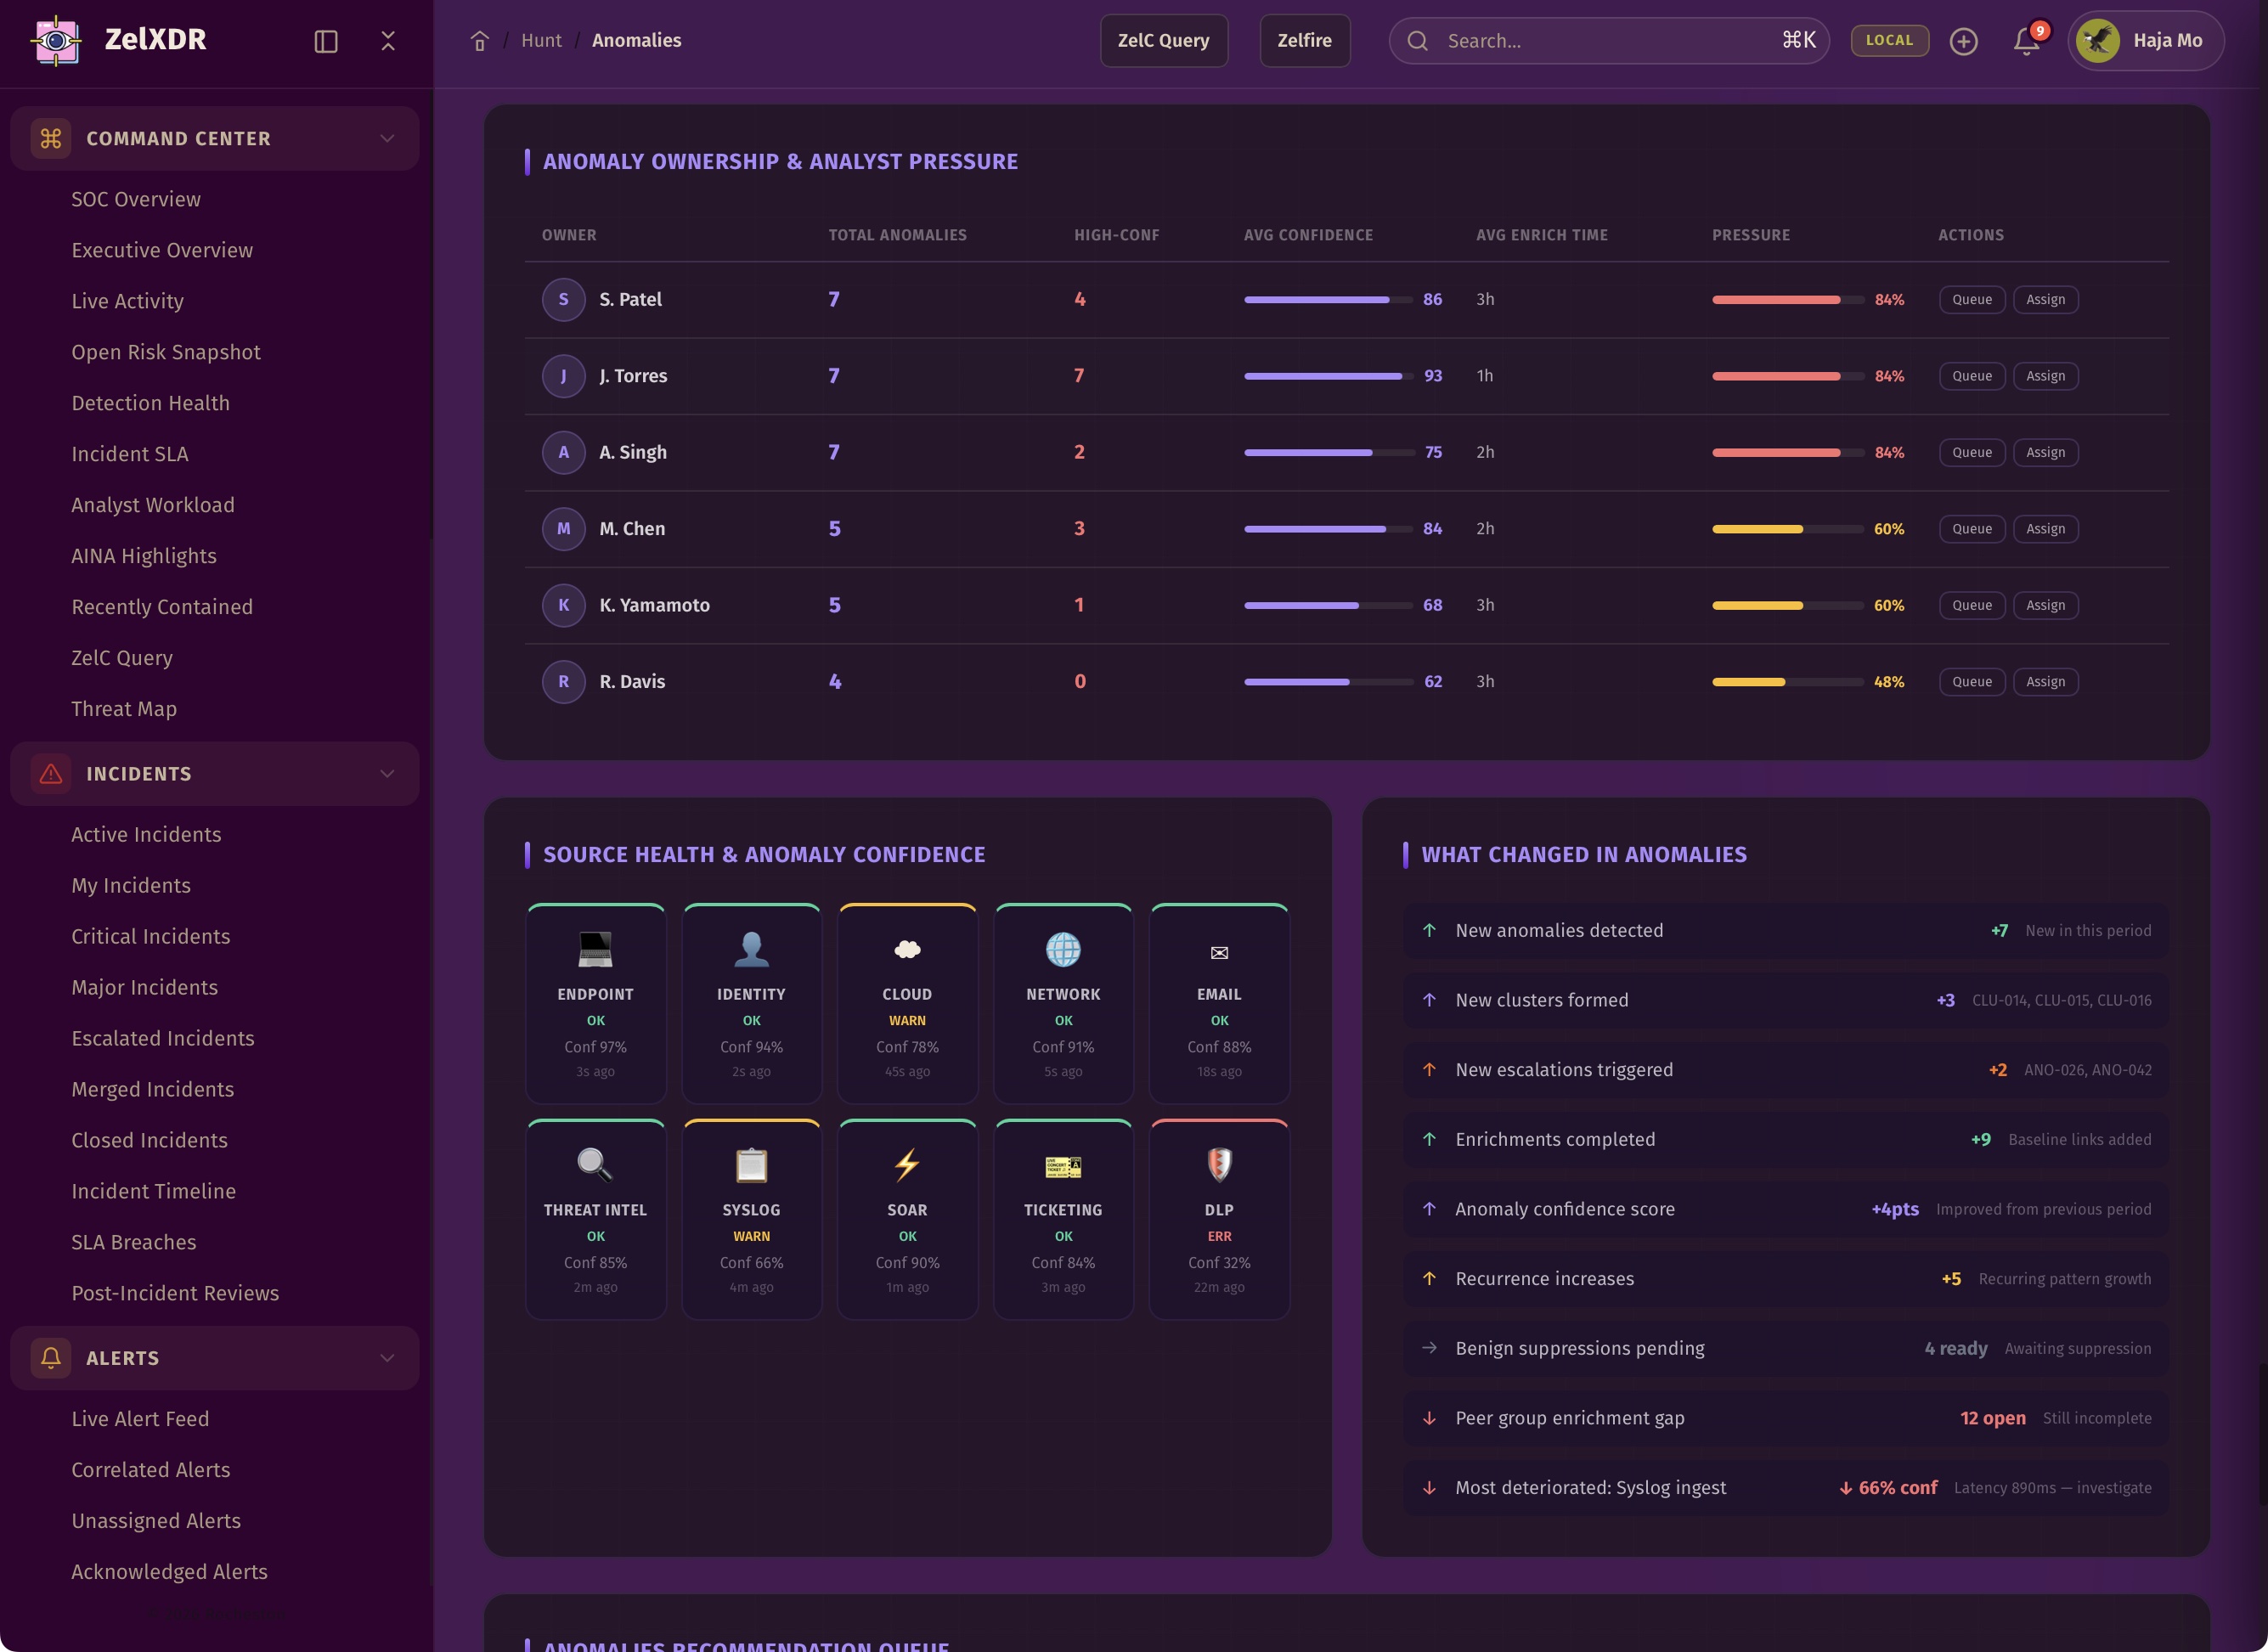
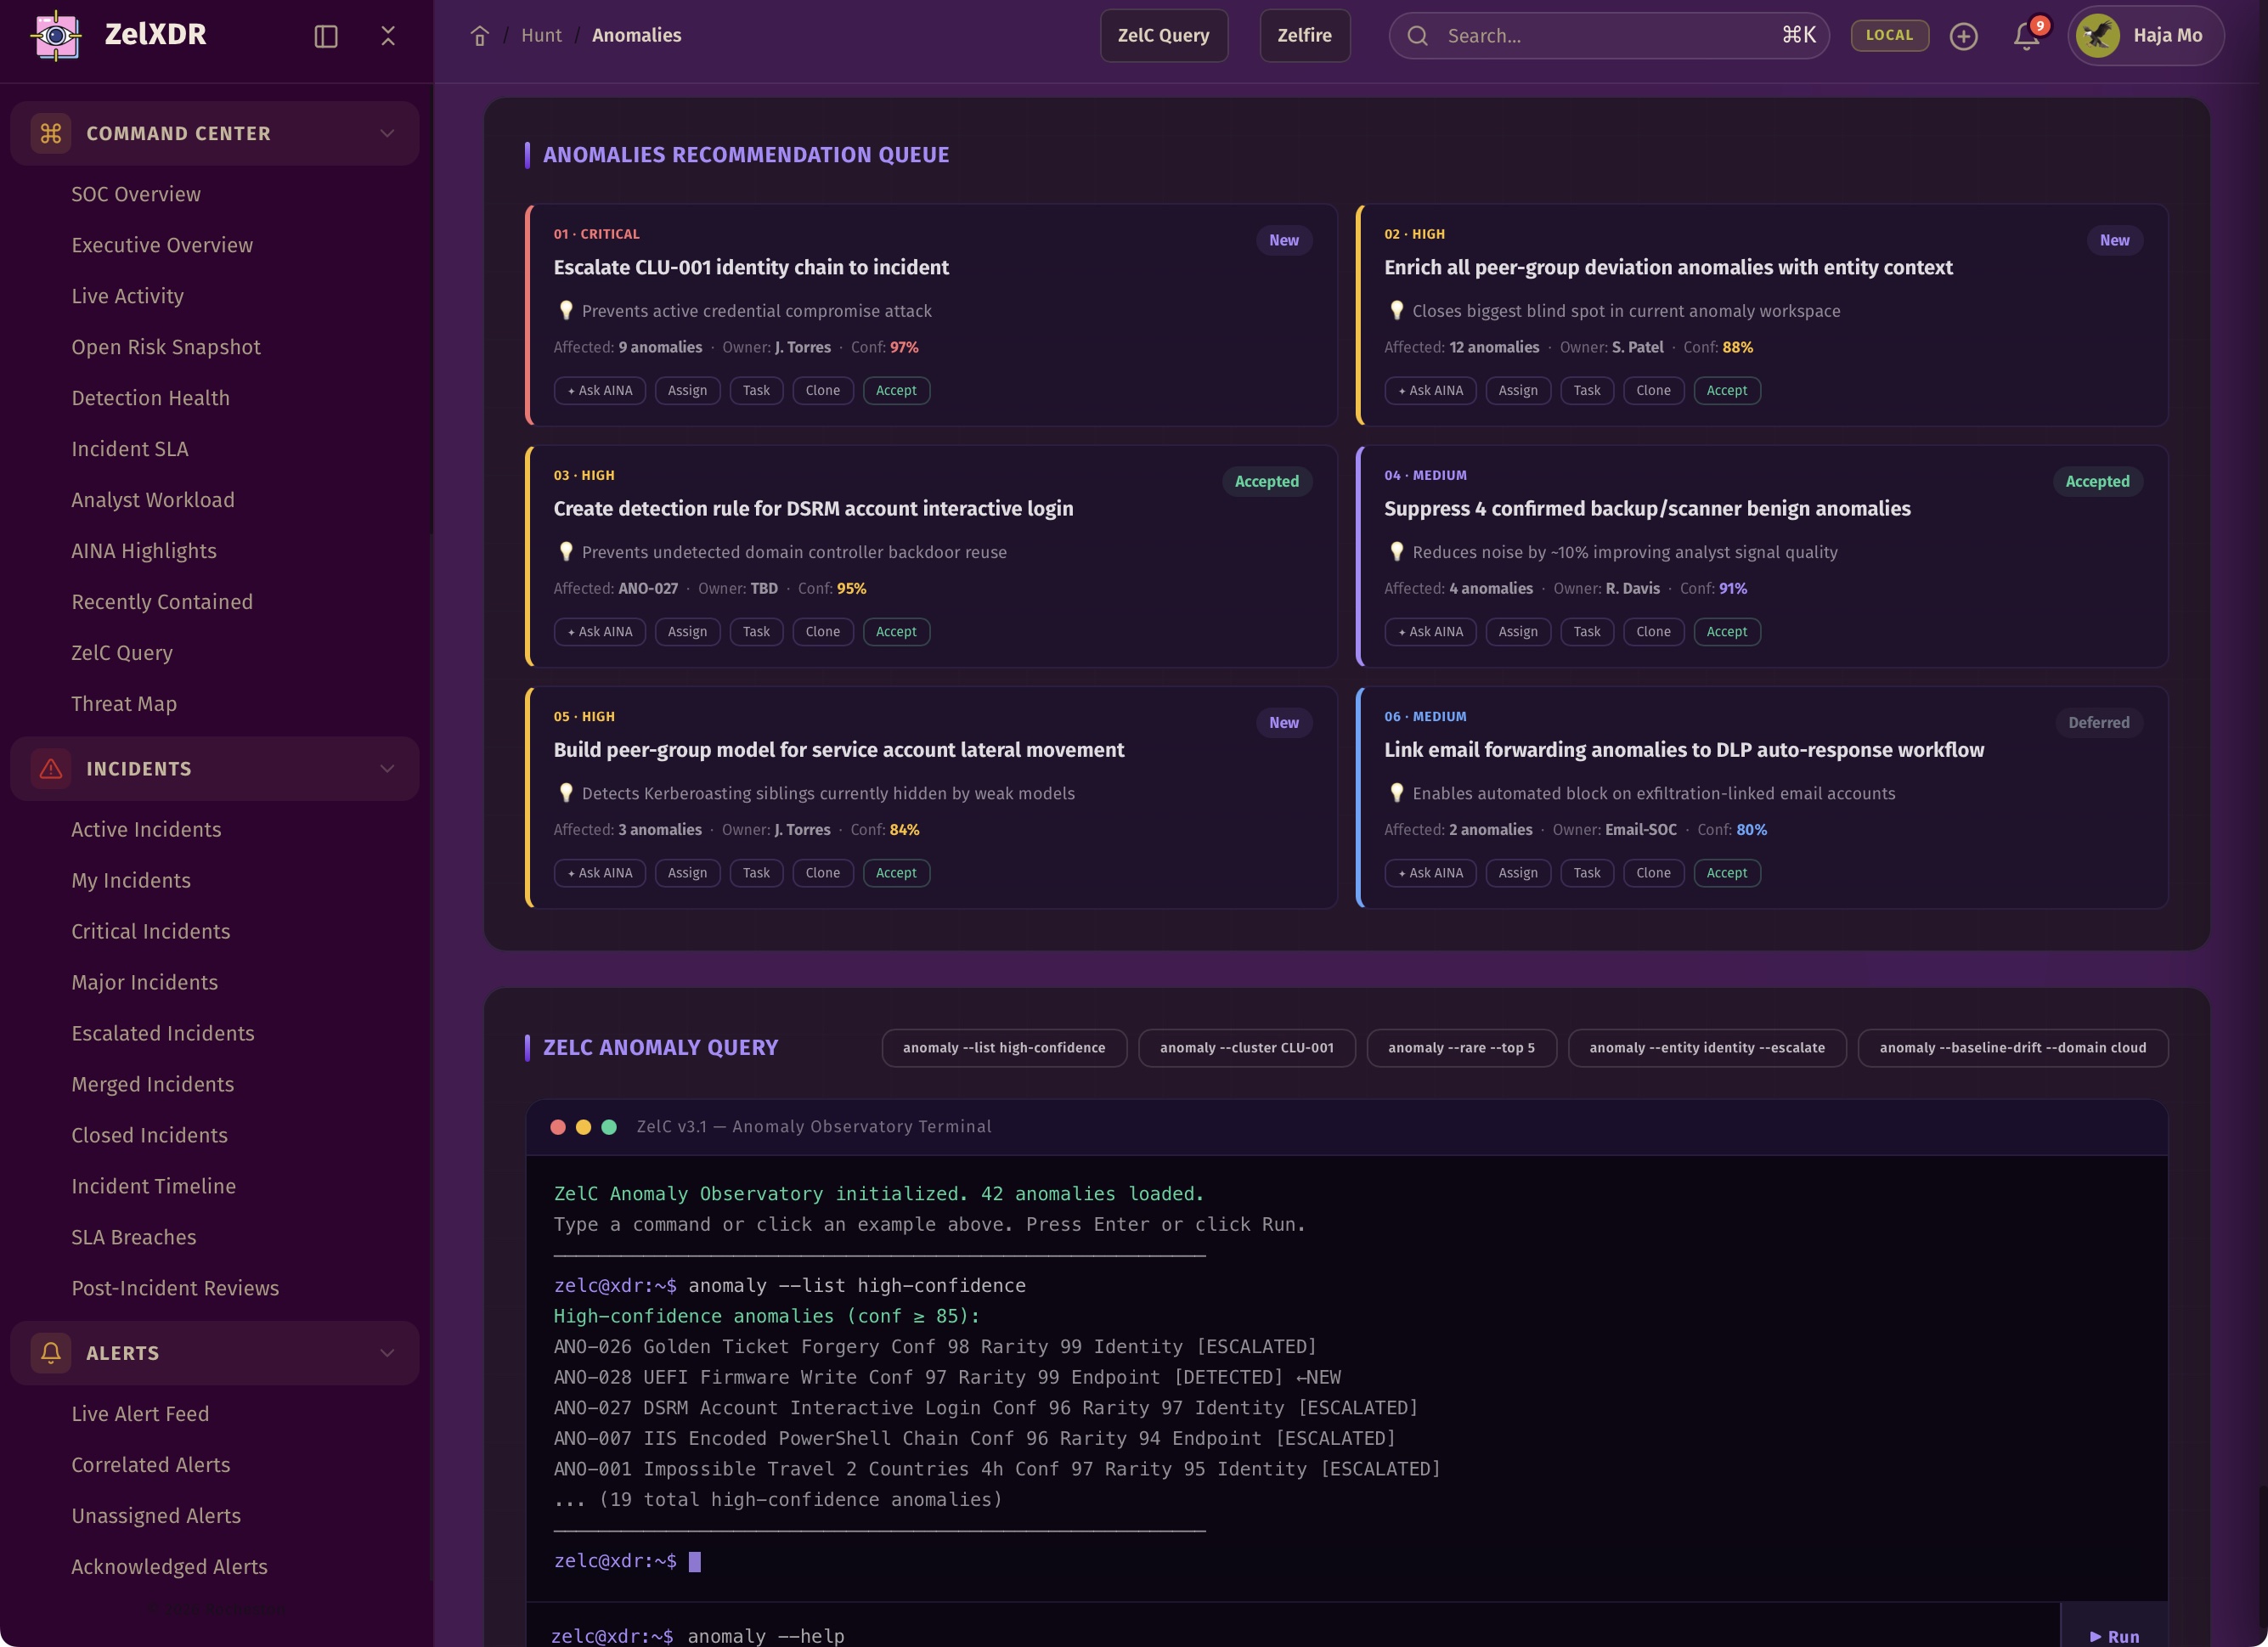
ZelXDR highlights meaningful anomalies, rare events, recurring deviations, and suspicious clusters while helping analysts understand what is truly risky and what is likely benign.
Anomalies matter when context proves they are dangerous.
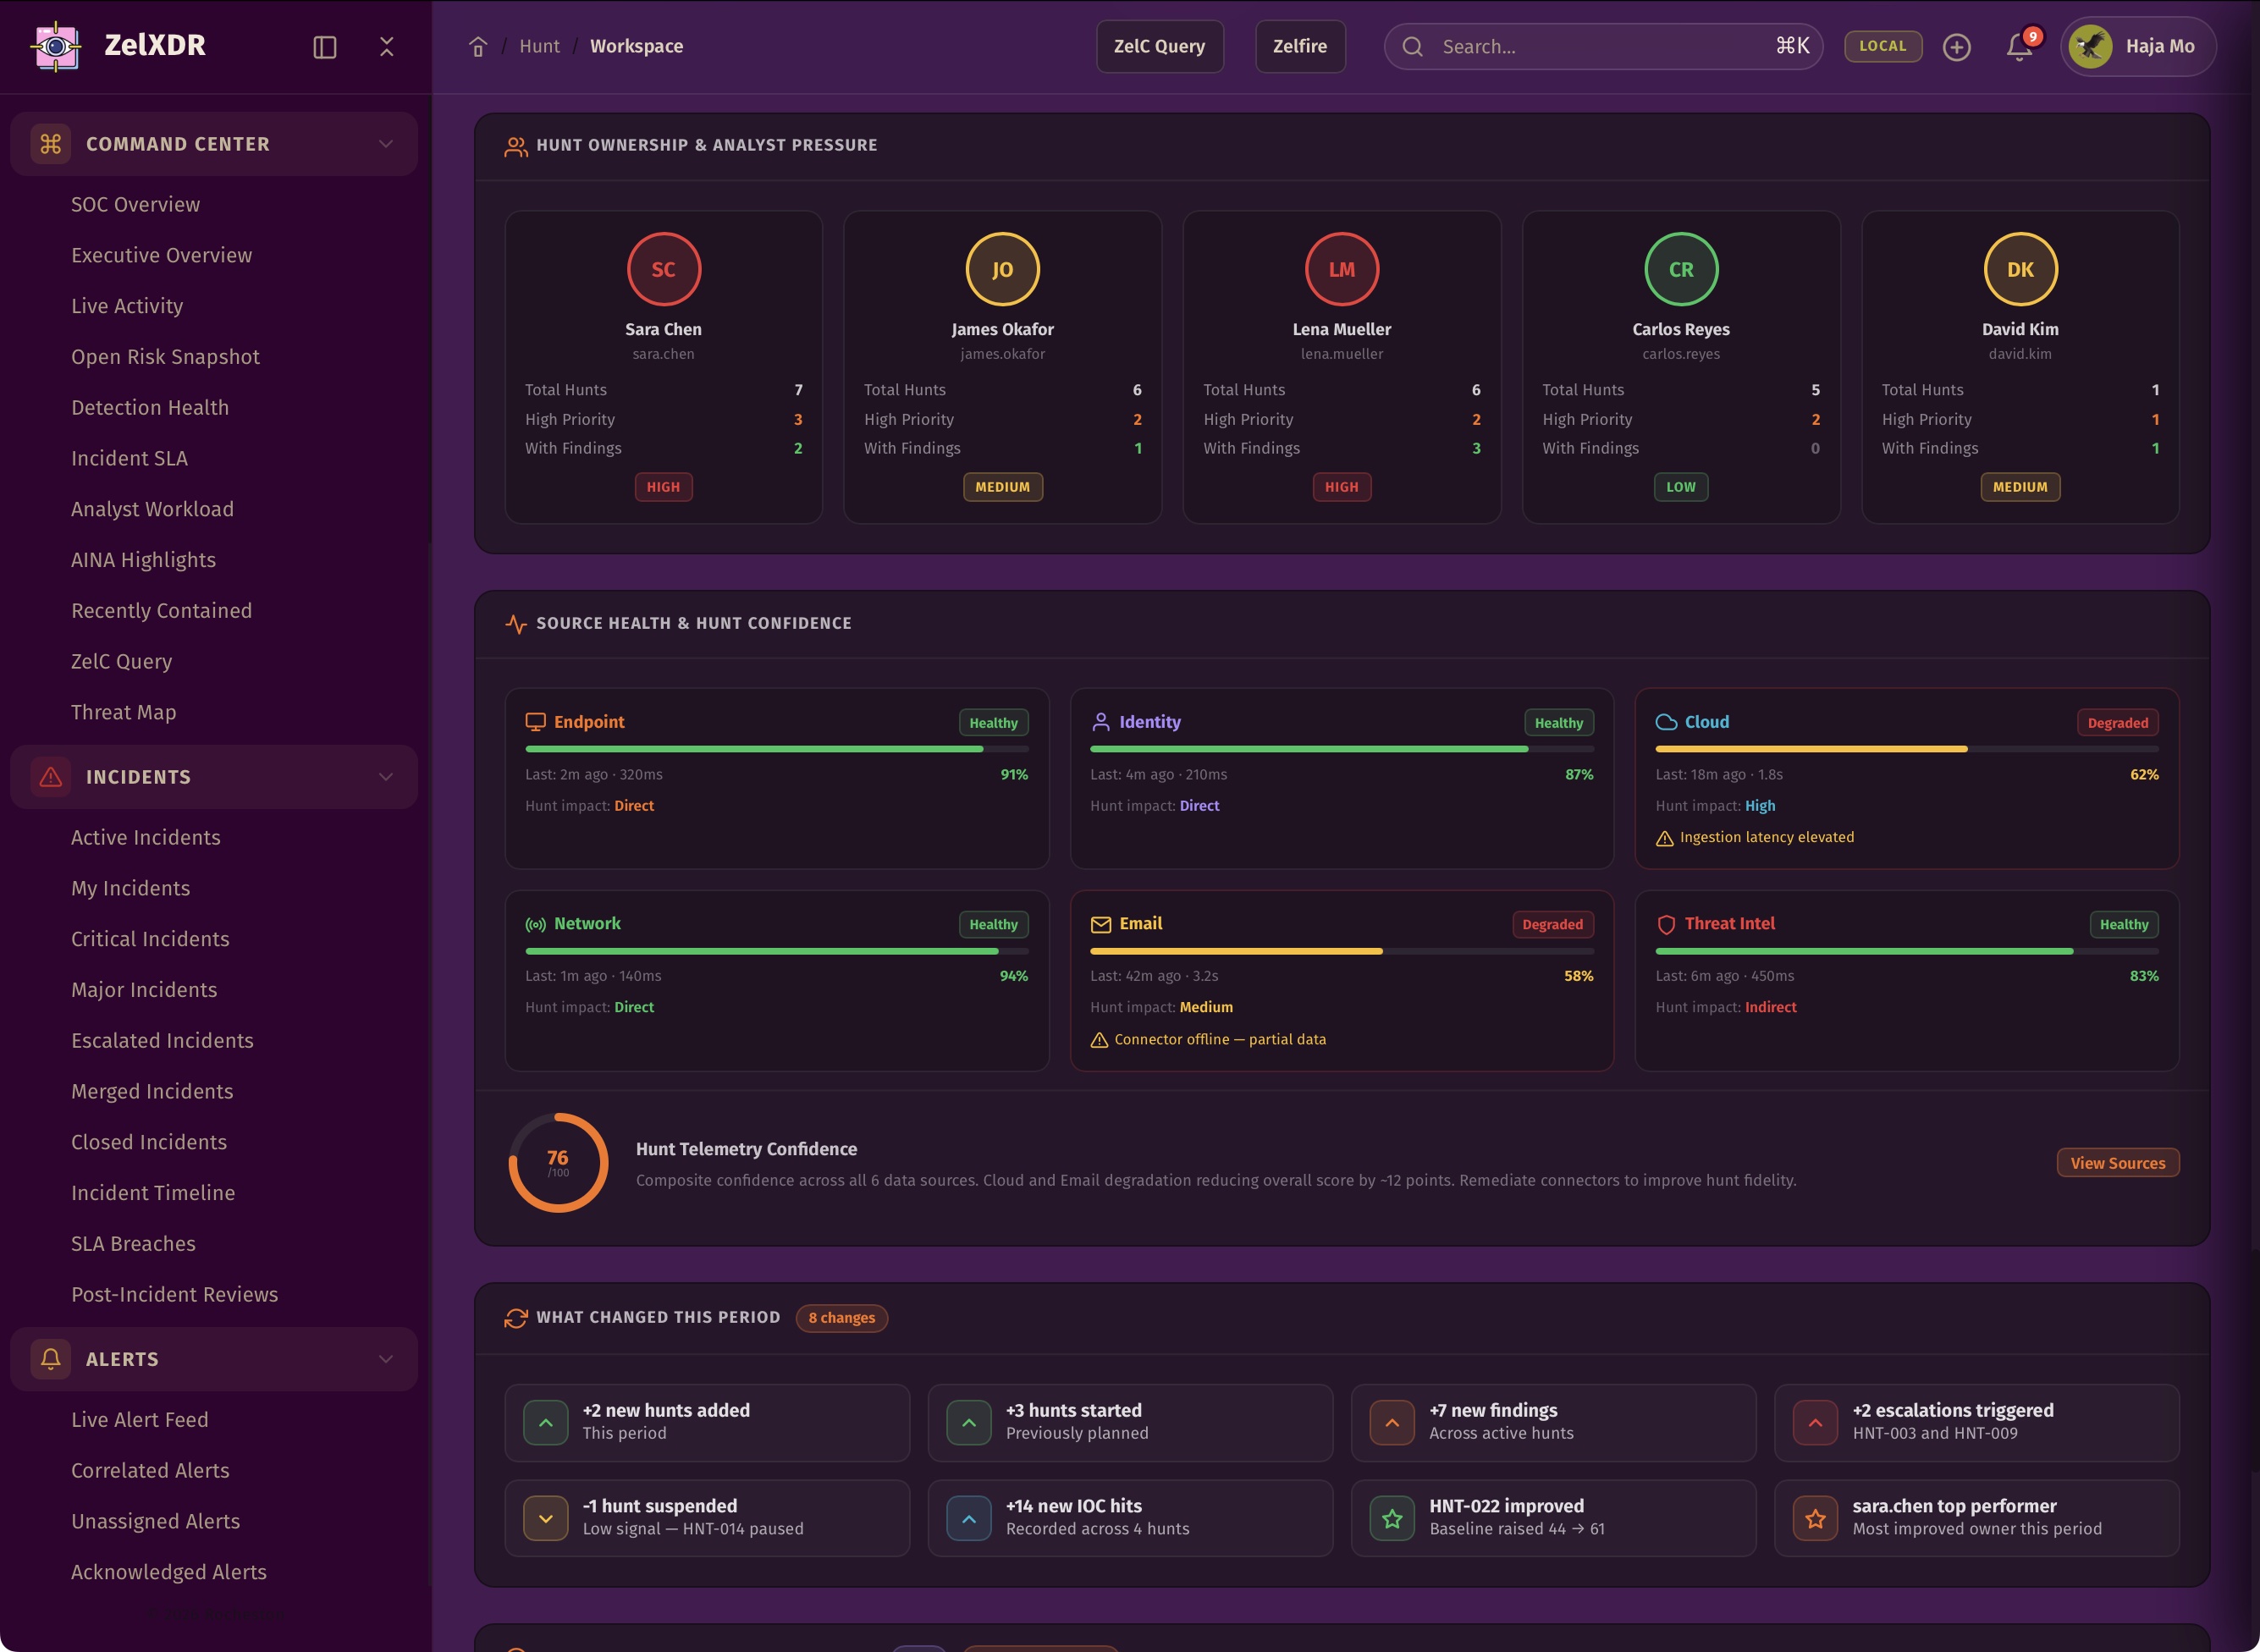
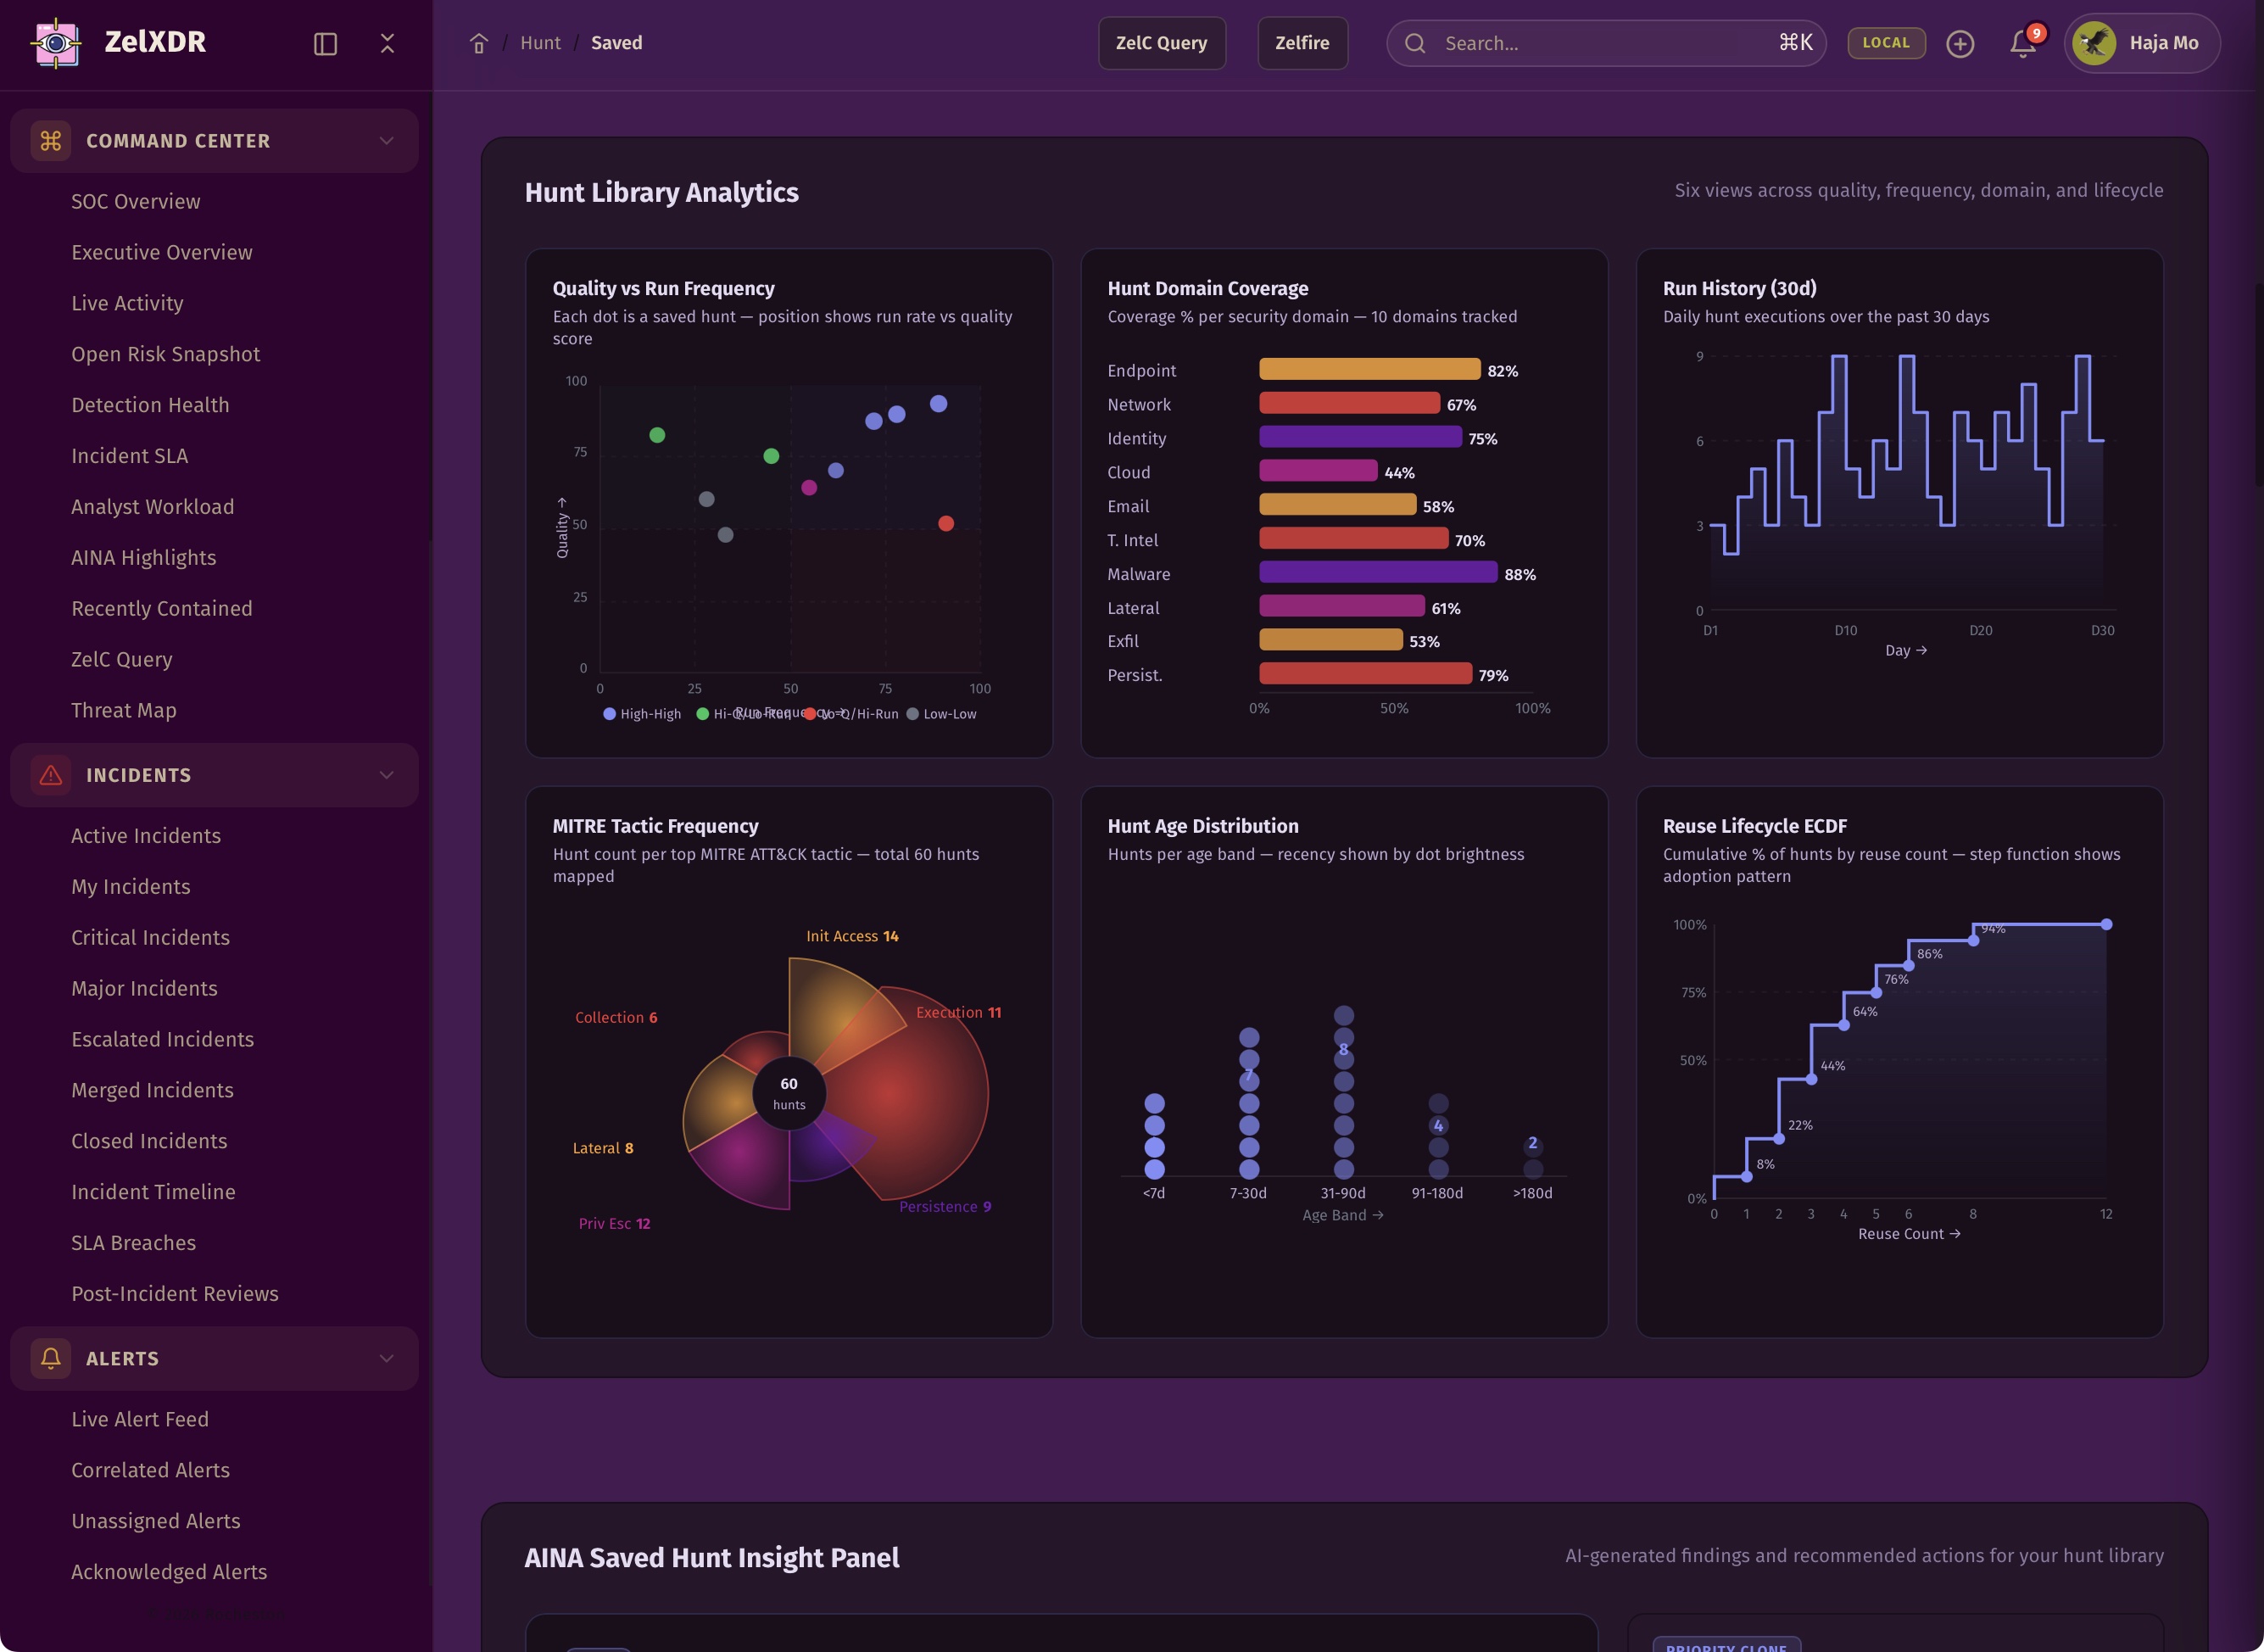
ZelXDR gives hunters a dedicated space to develop hypotheses, explore evidence, run pivots, review findings, and convert discoveries into incidents, notes, and reusable intelligence.
Hunting is not random searching. It is focused curiosity.
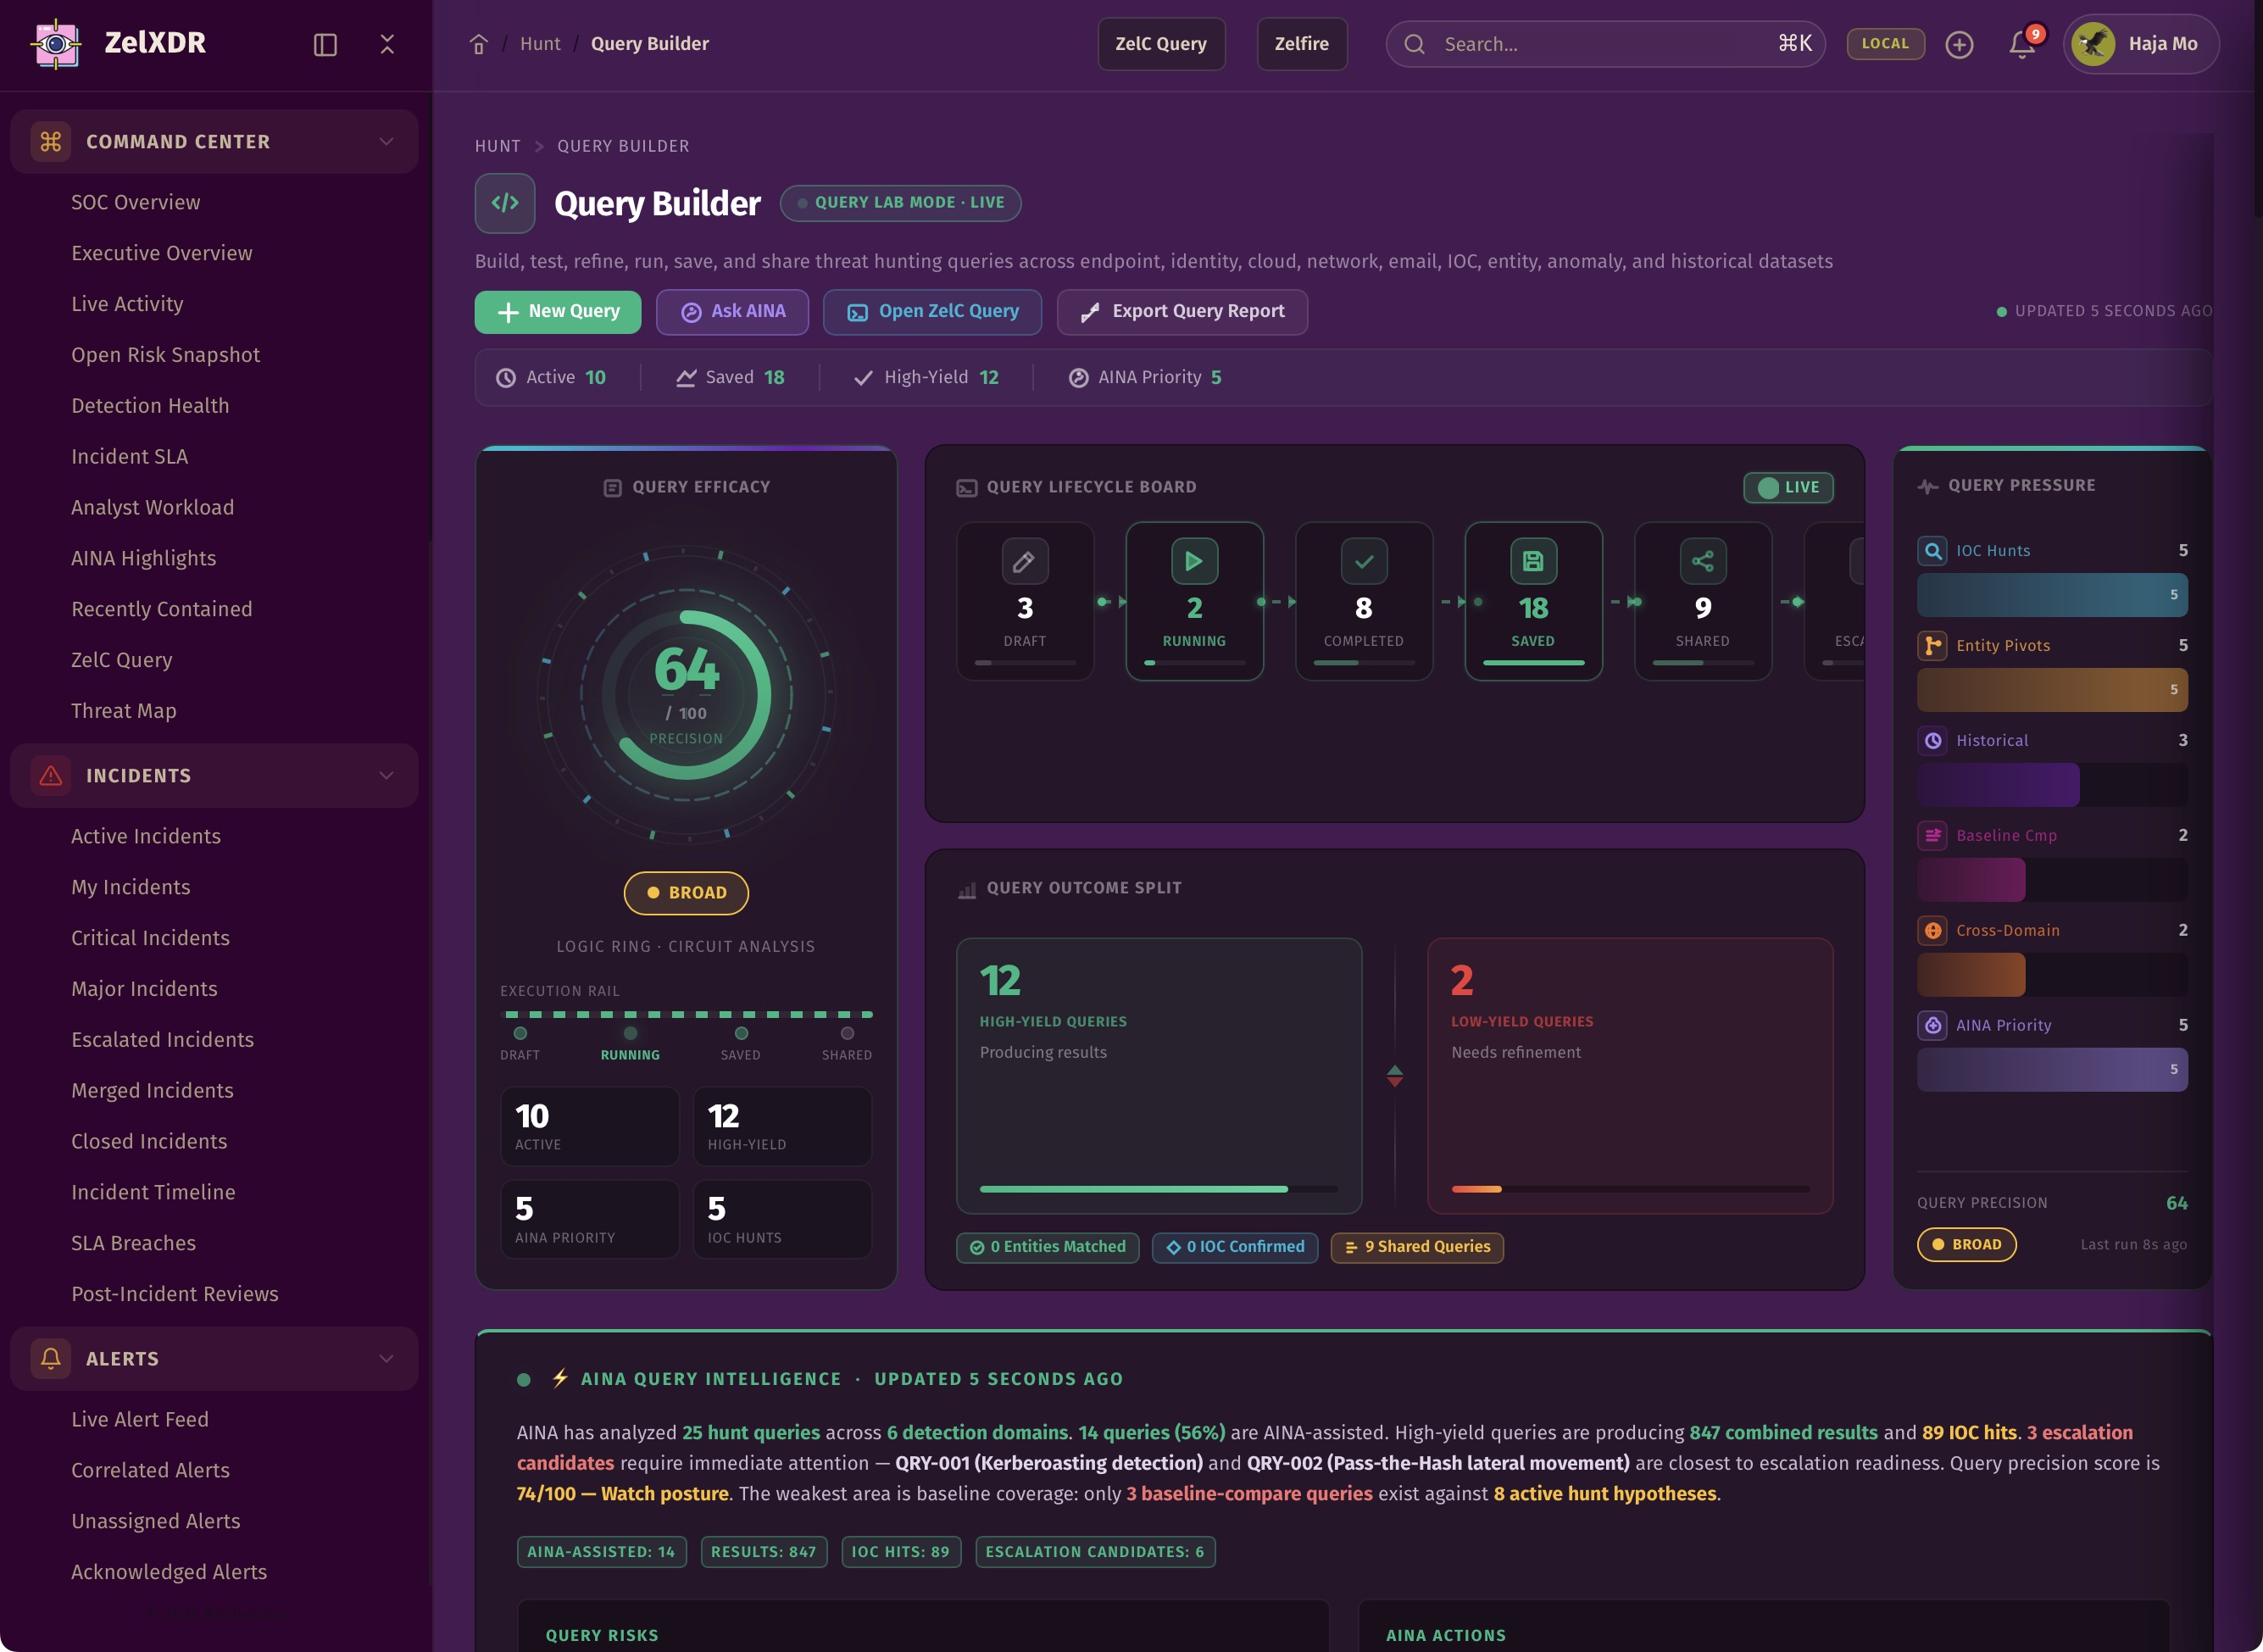
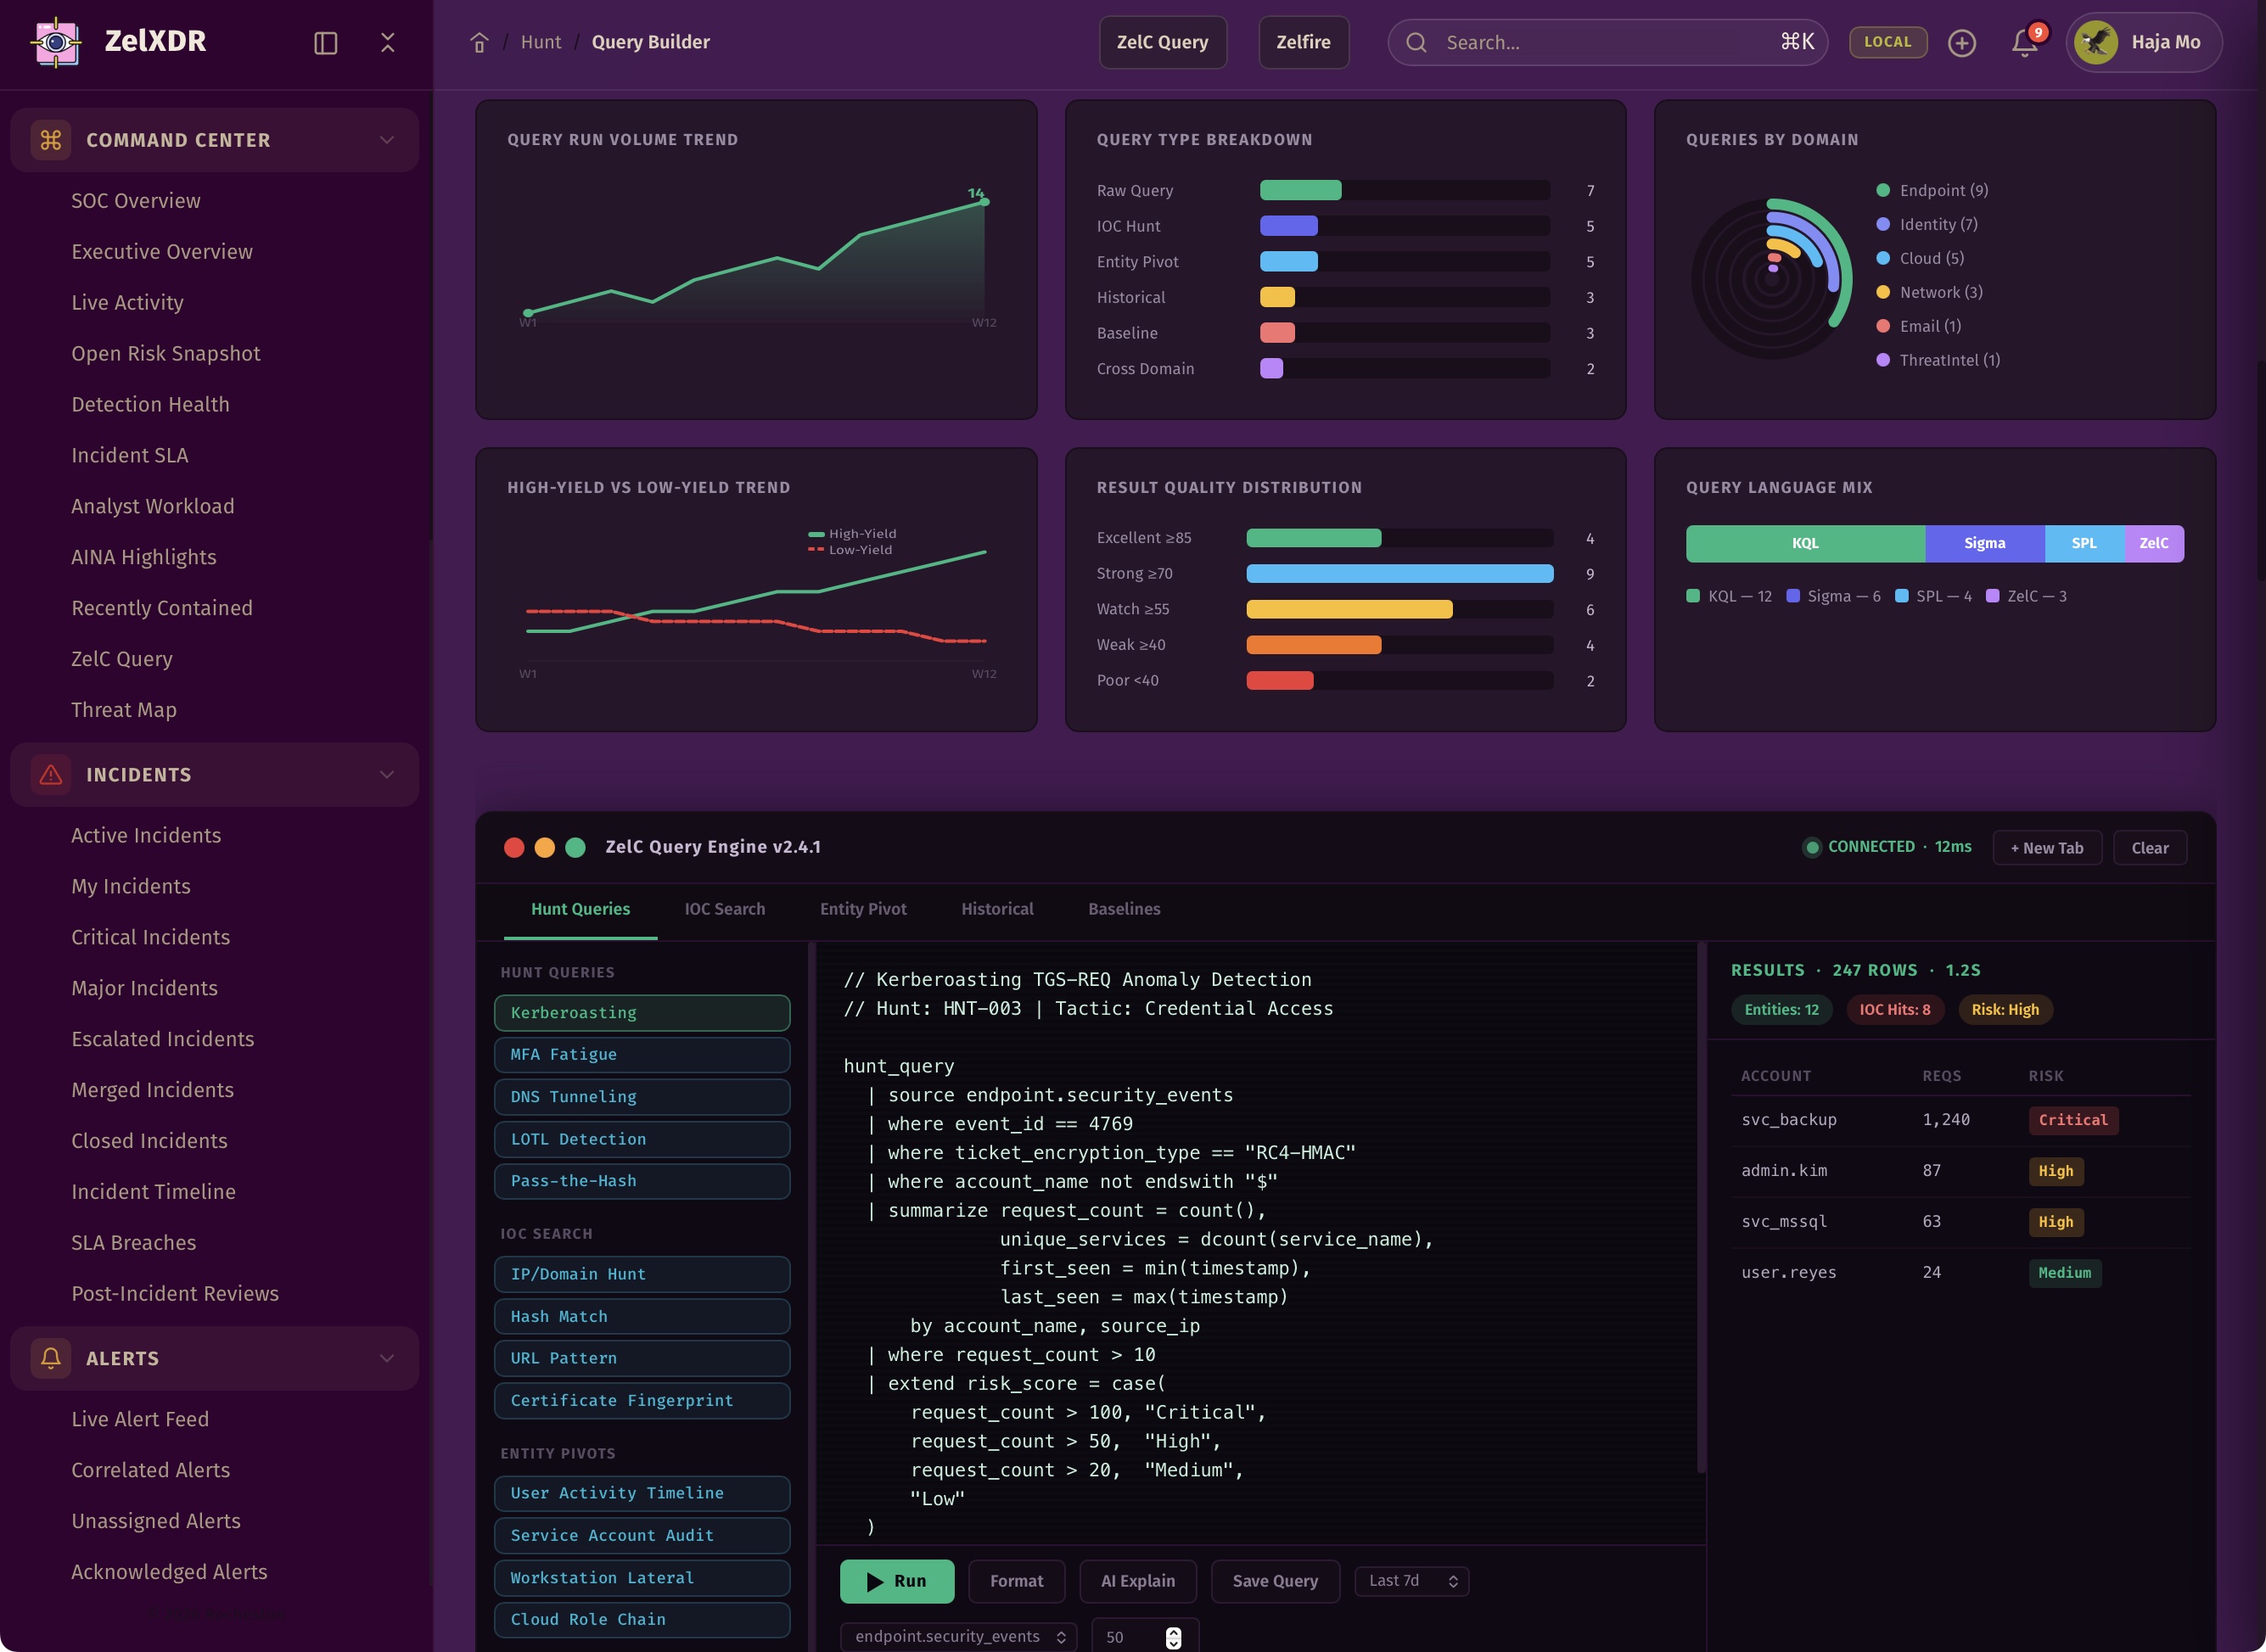
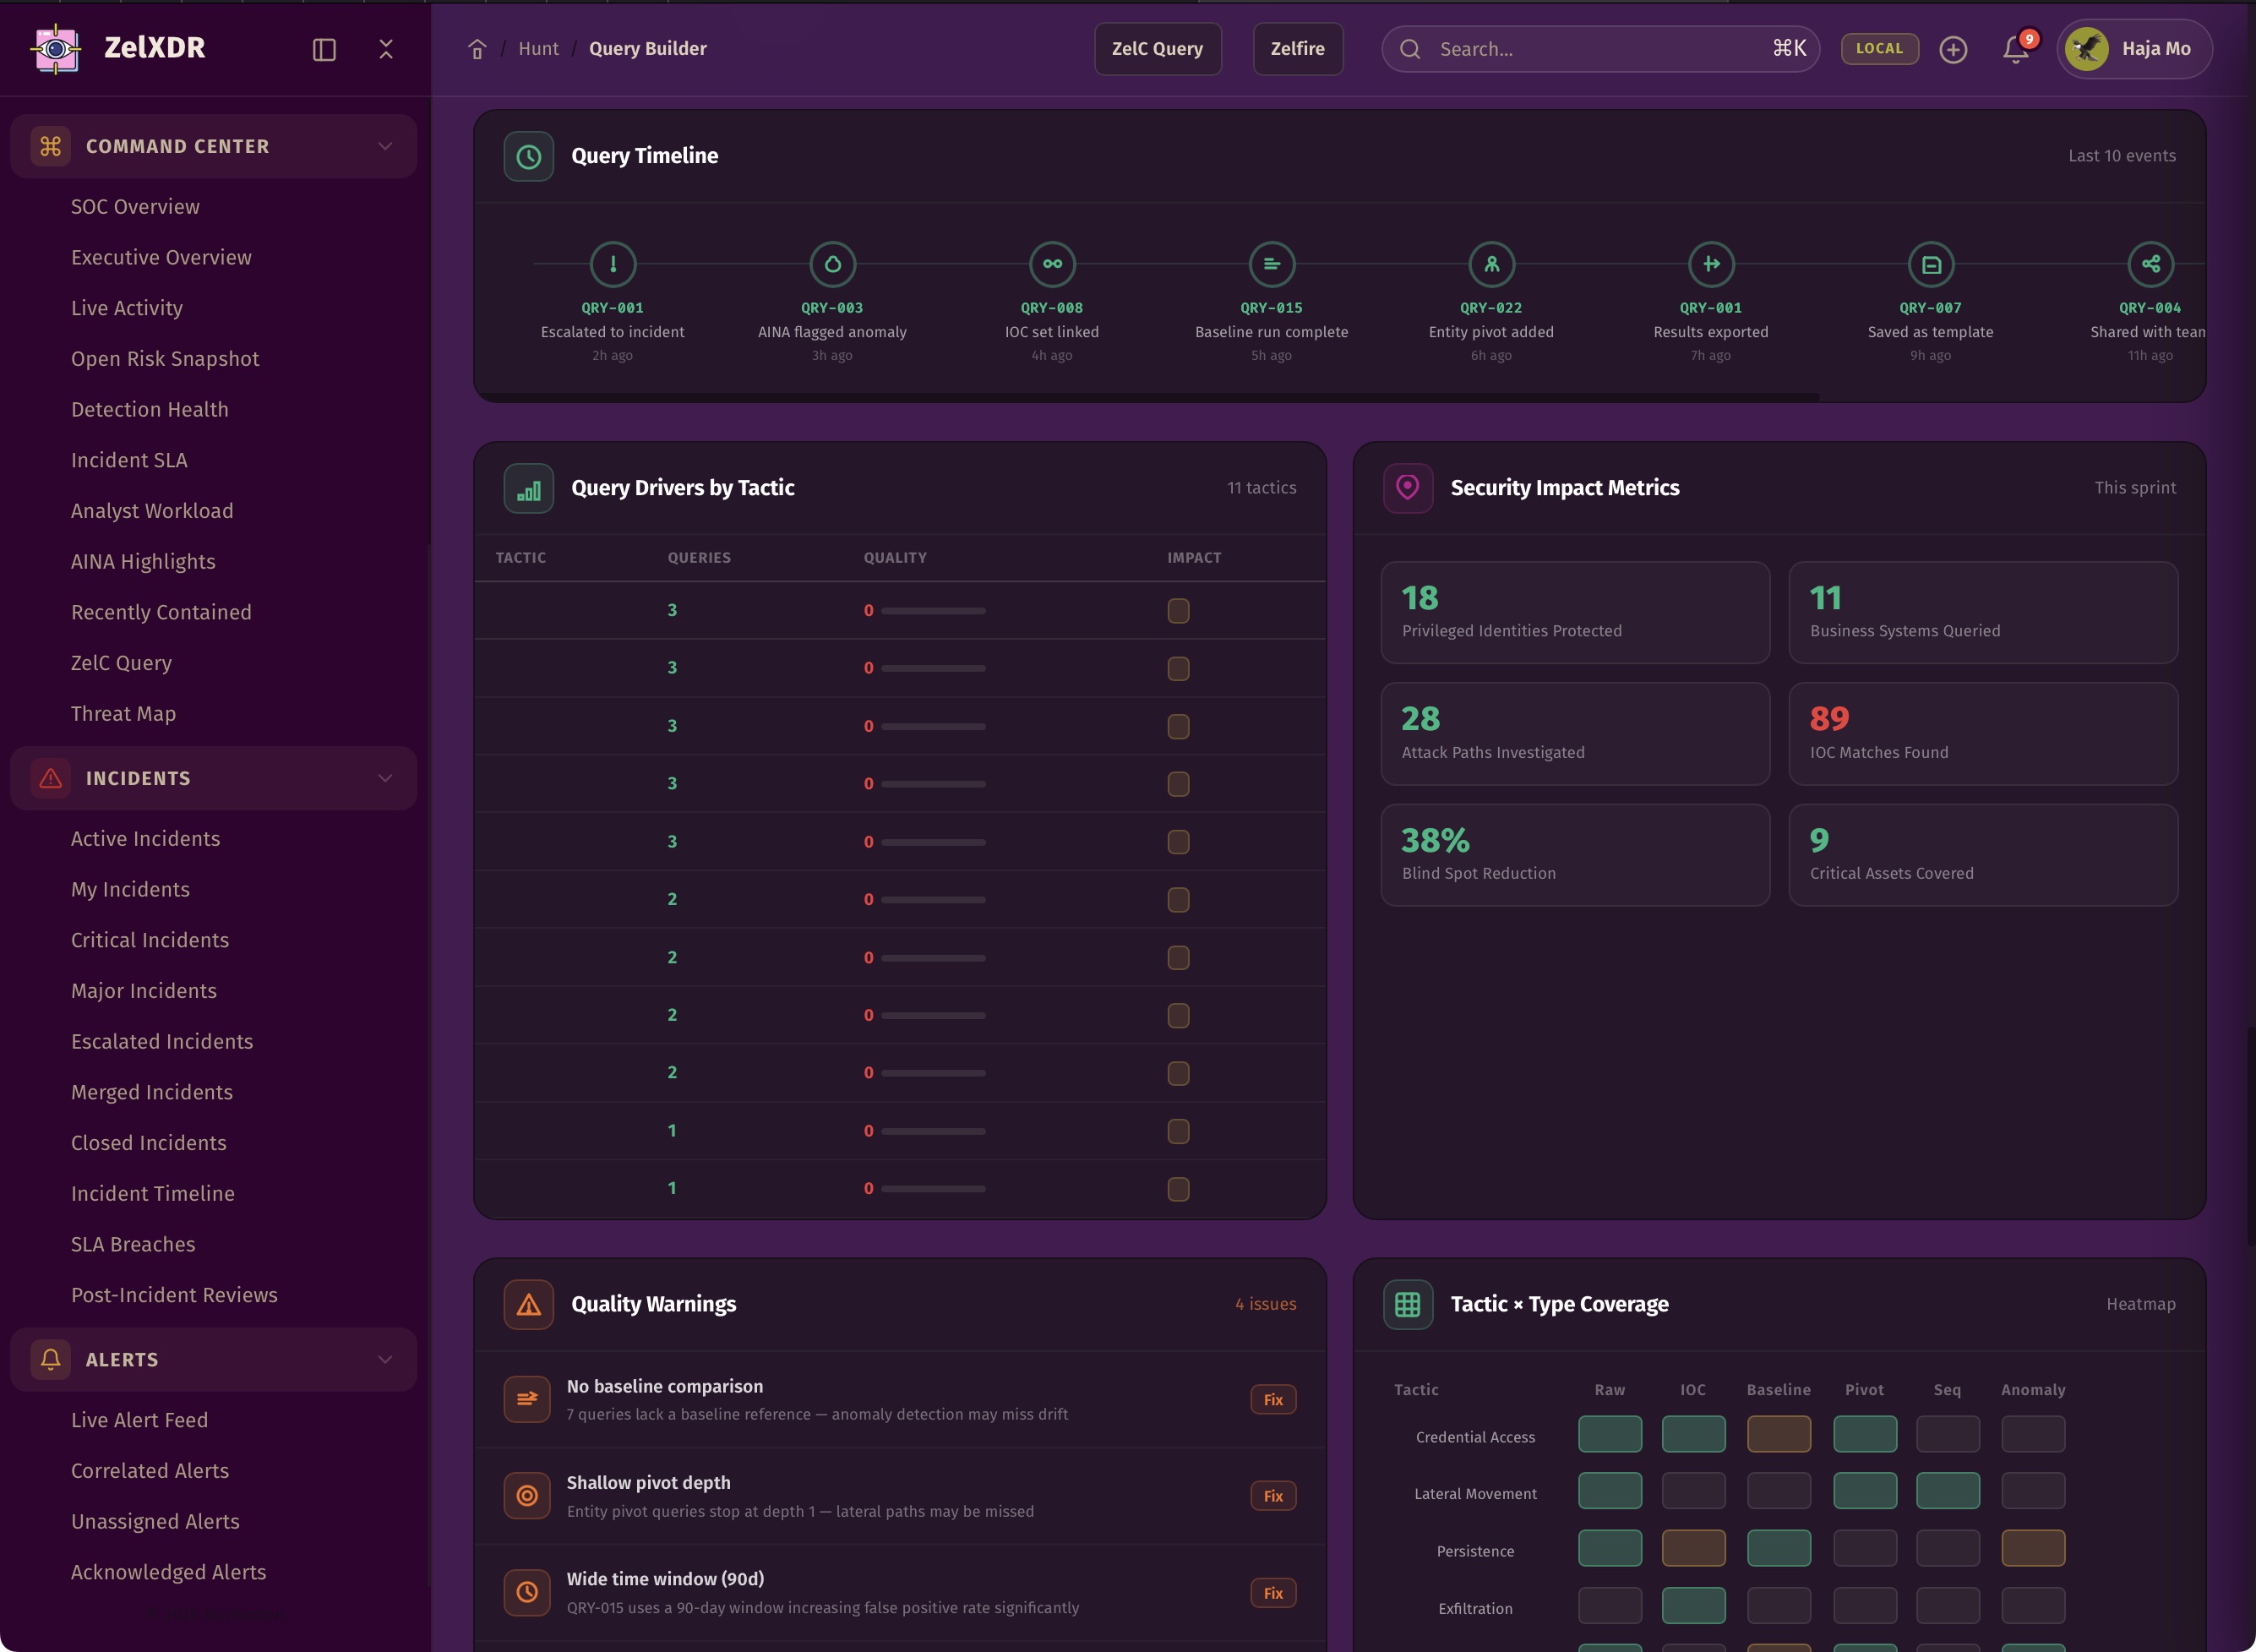
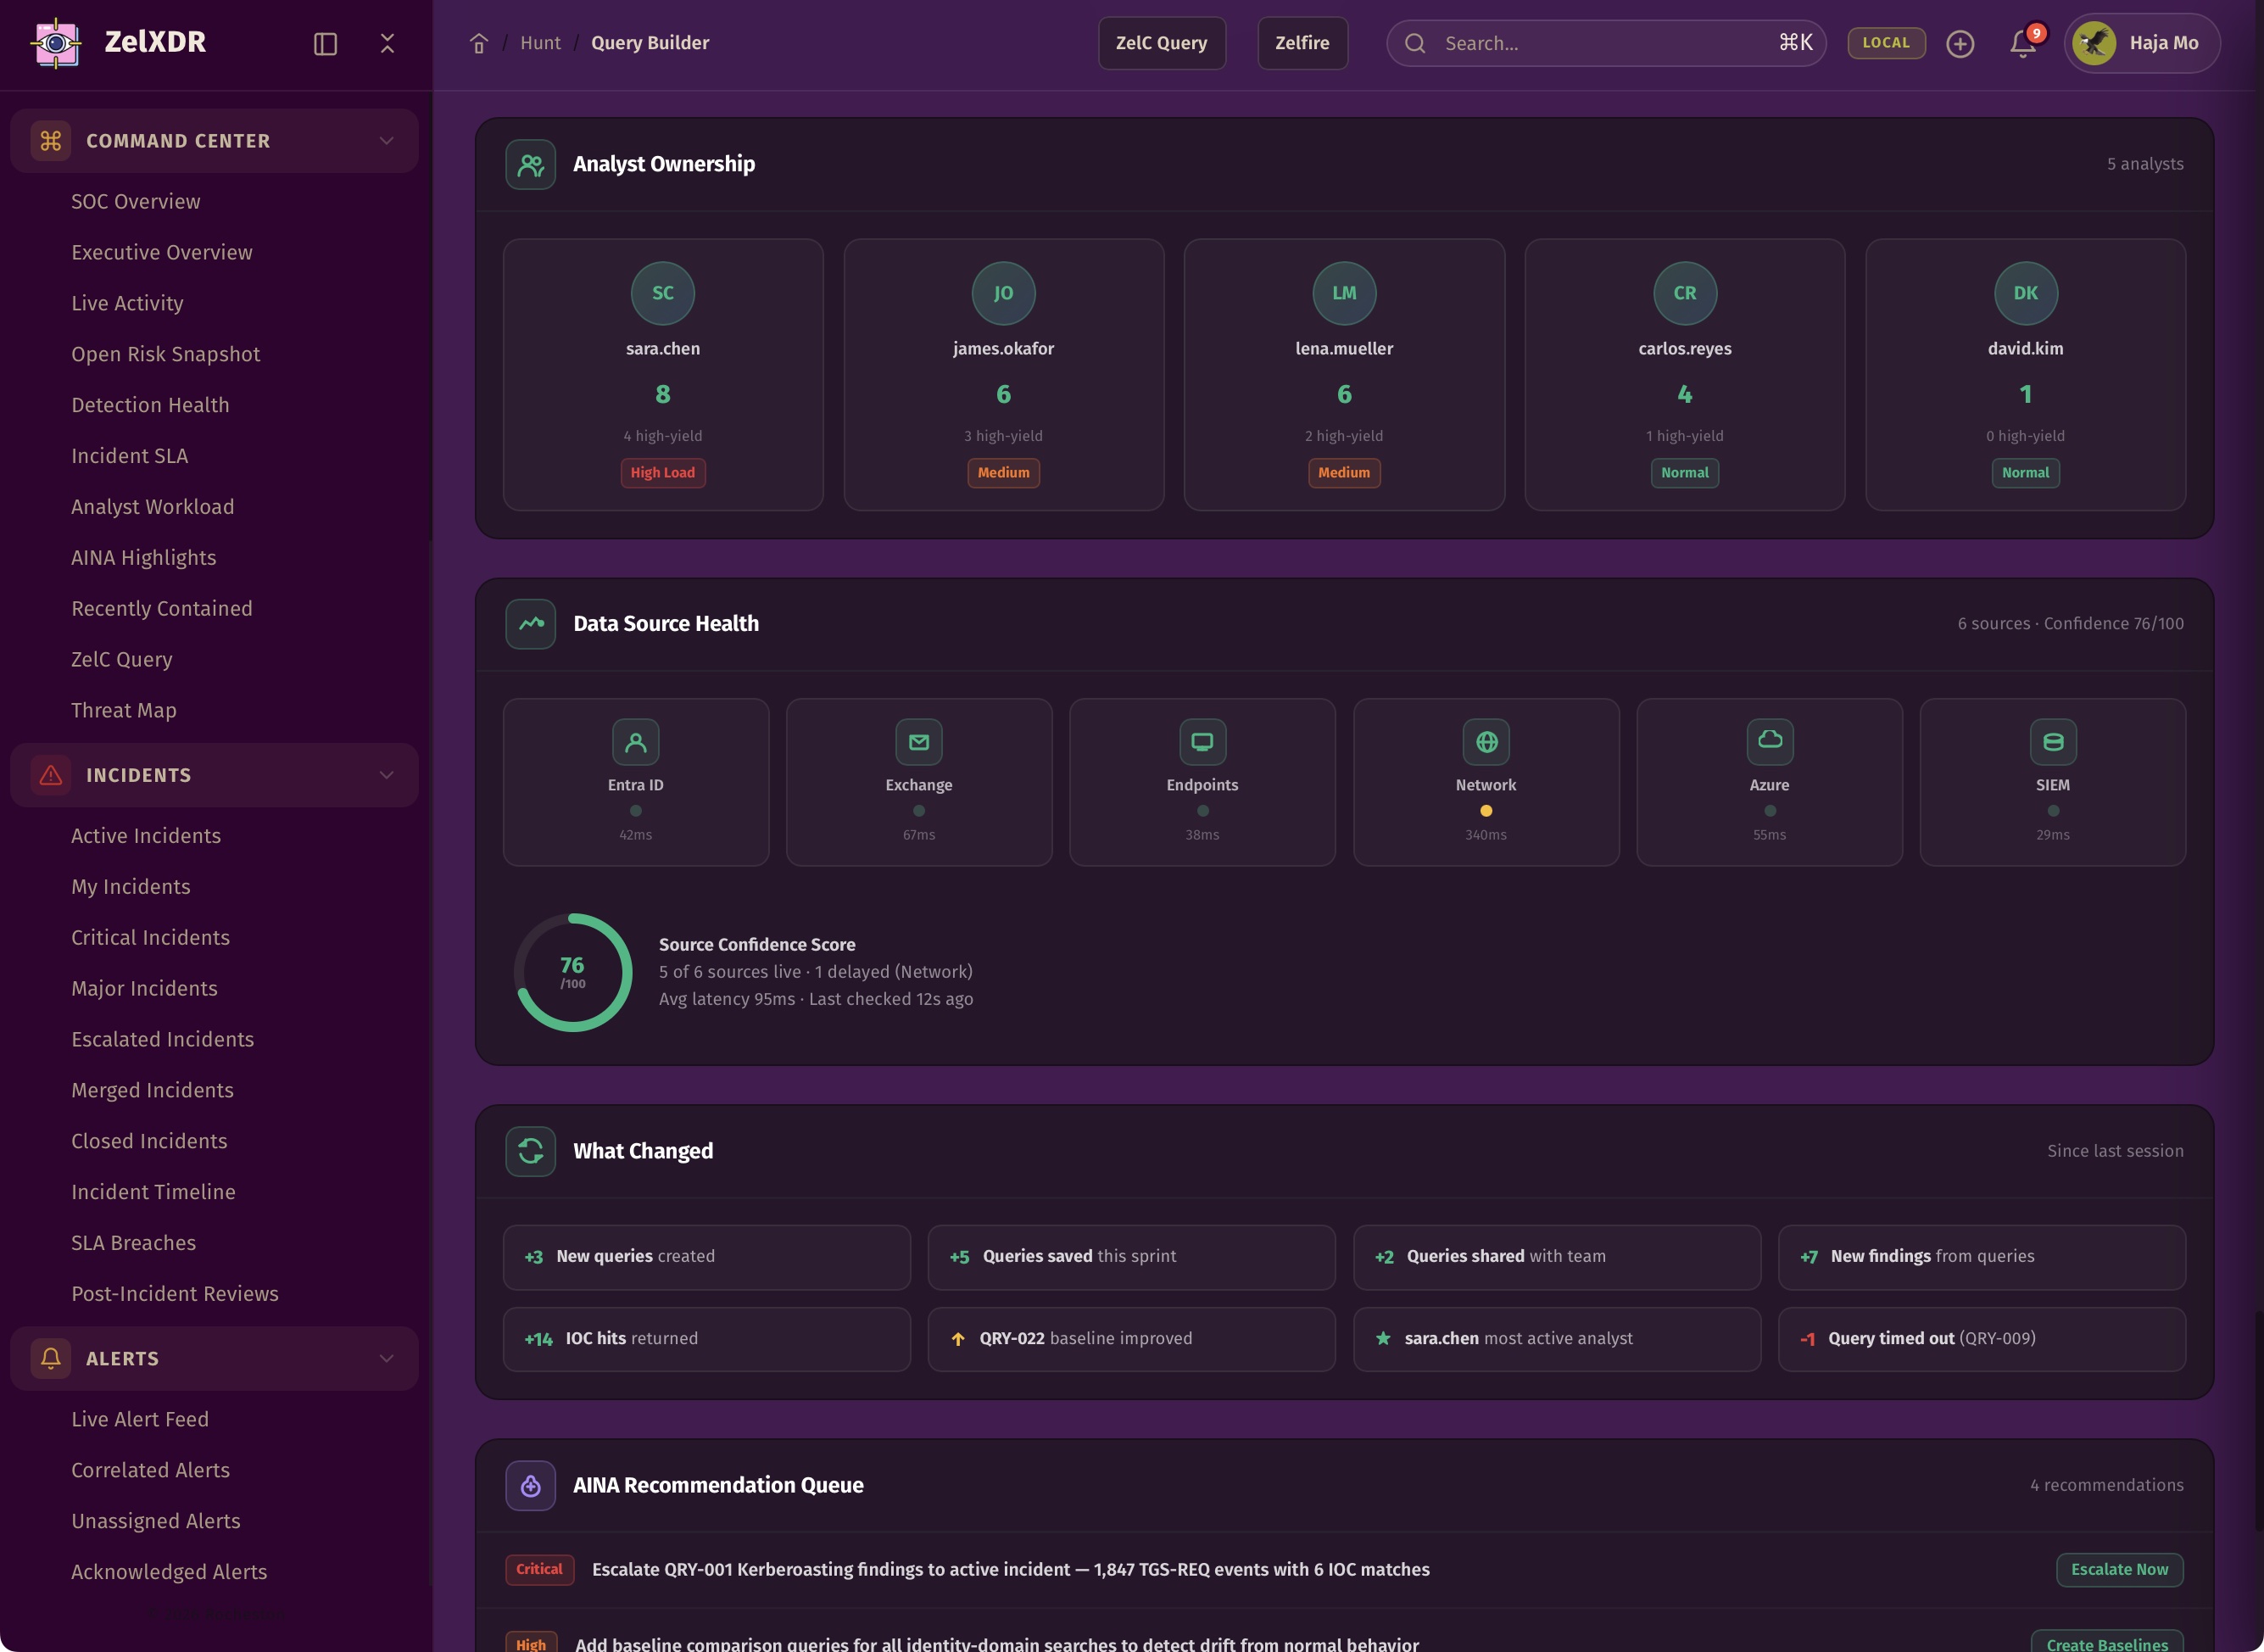
The Query Builder offers a premium editor and workflow for writing, testing, refining, and saving hunt logic. It helps teams move from ideas to repeatable search intelligence quickly.
A strong query is a disciplined form of thinking.
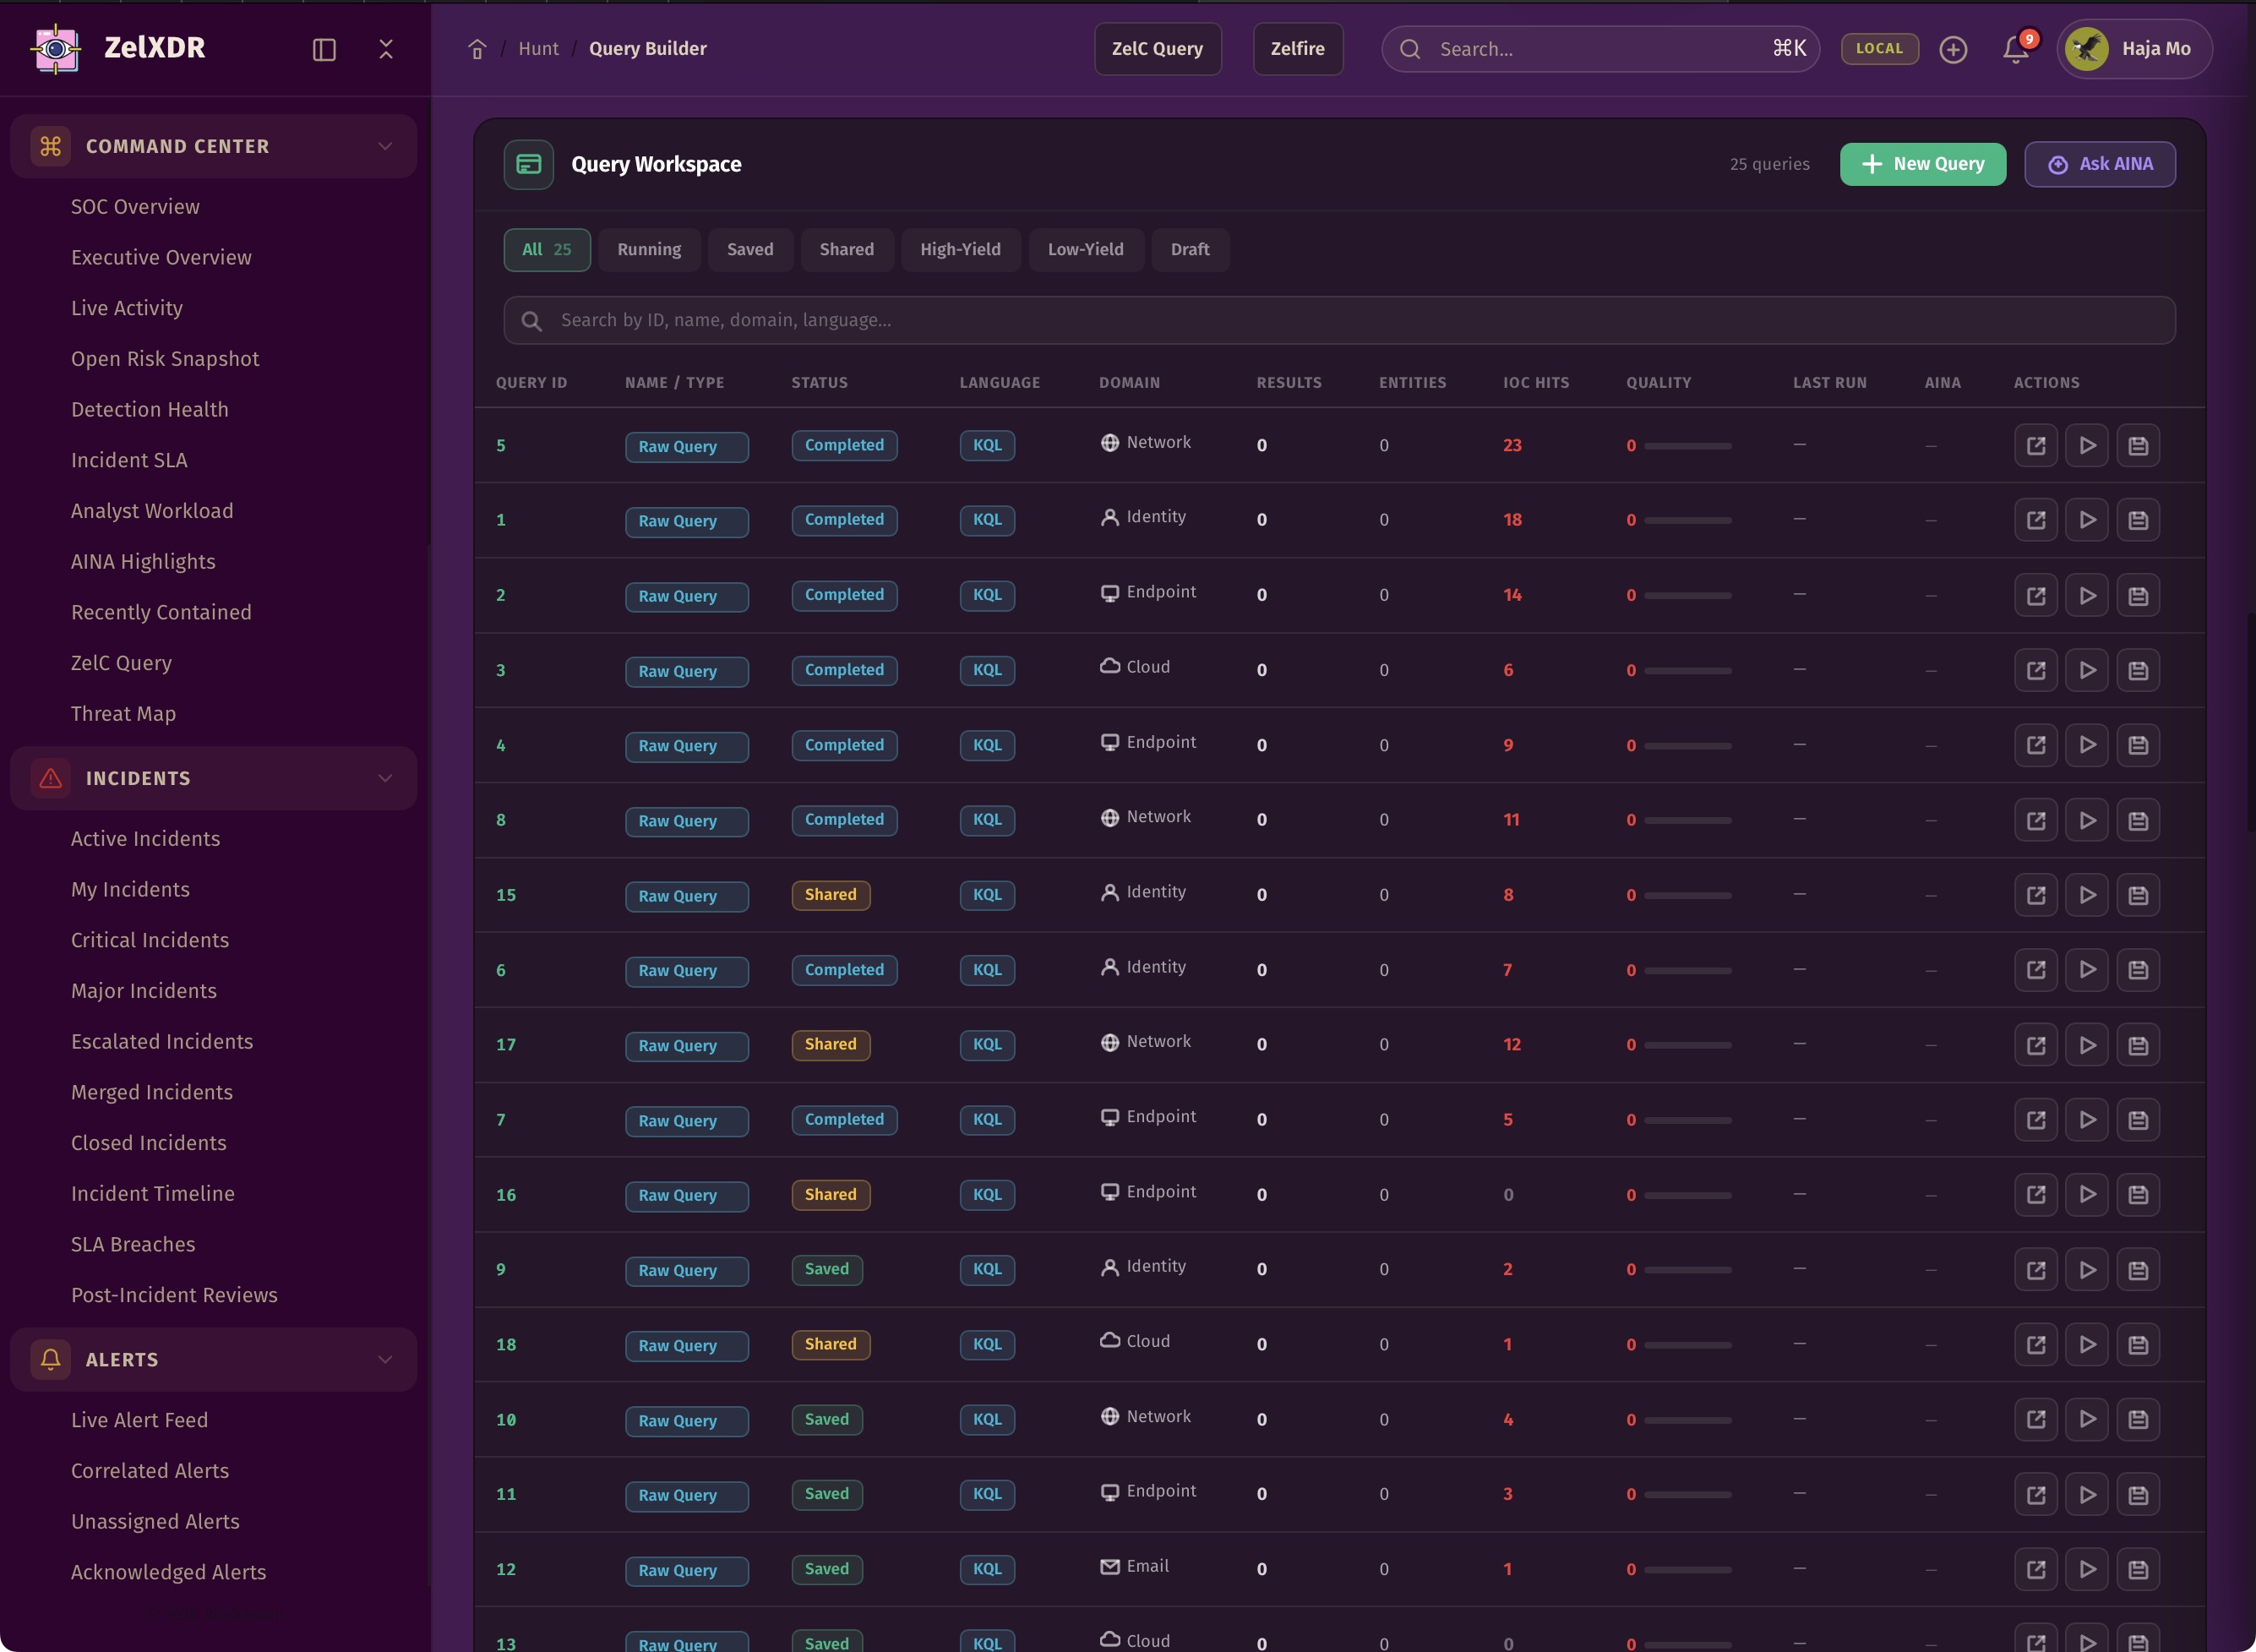
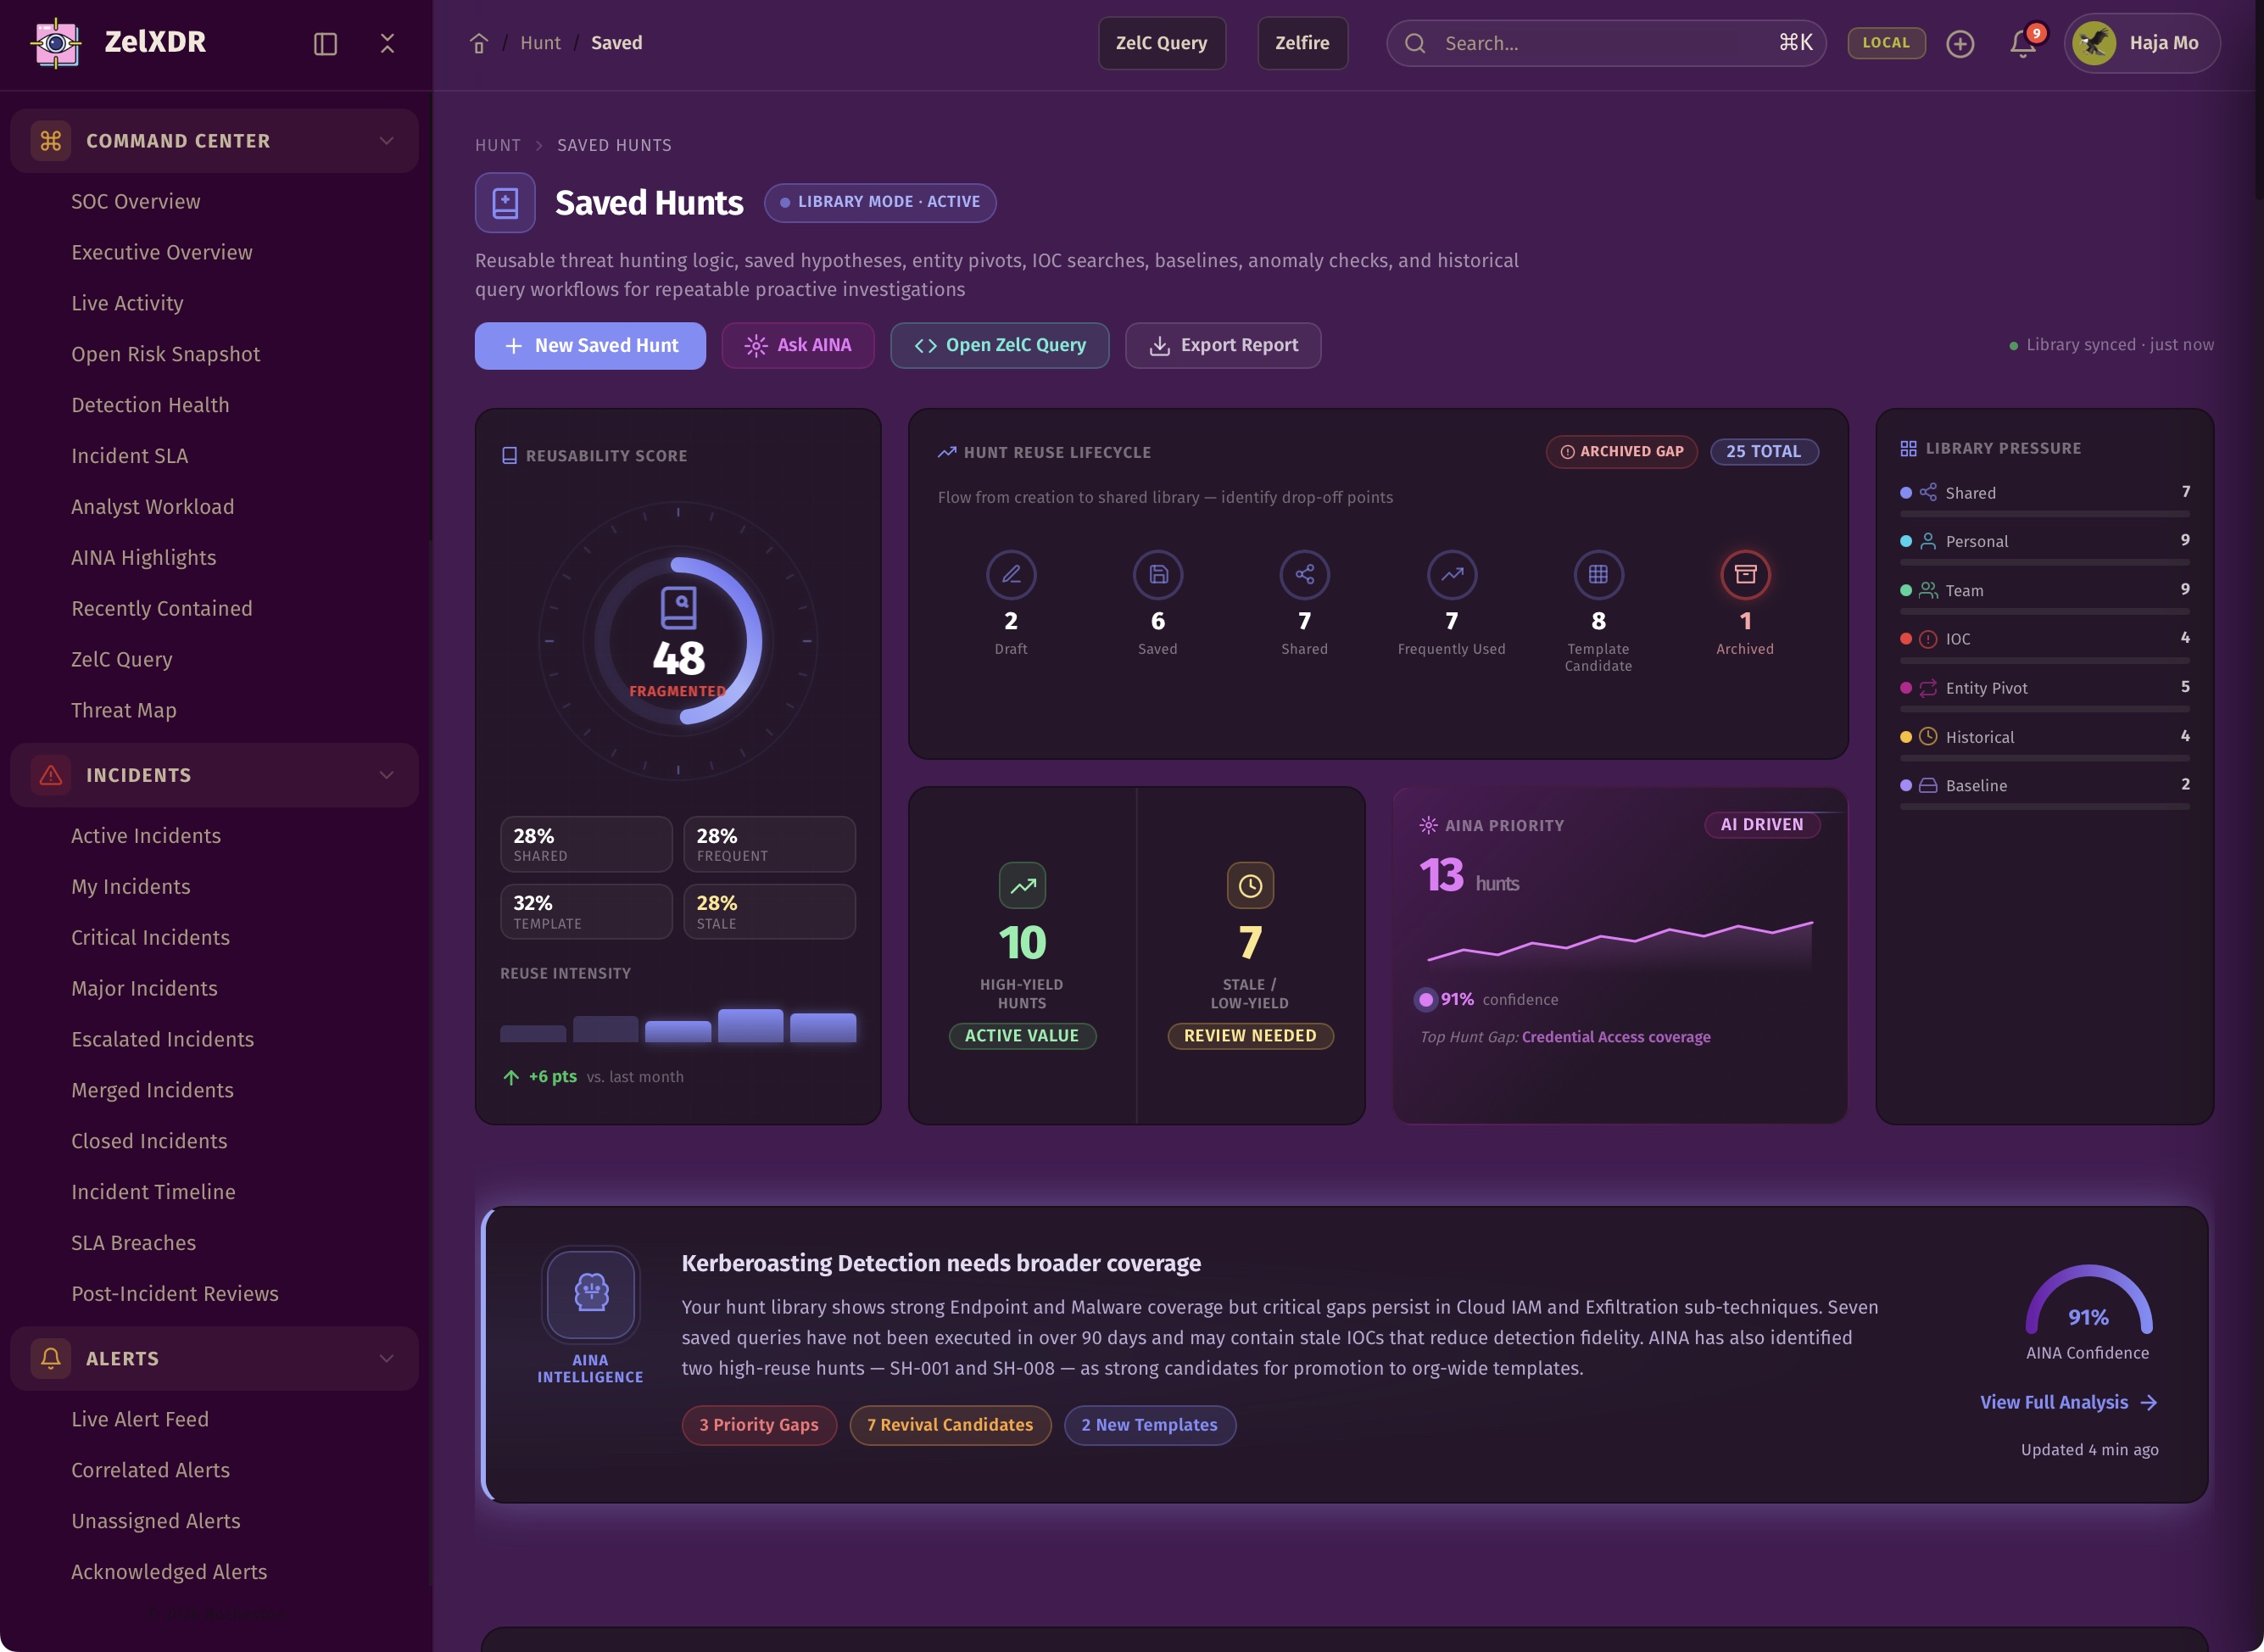
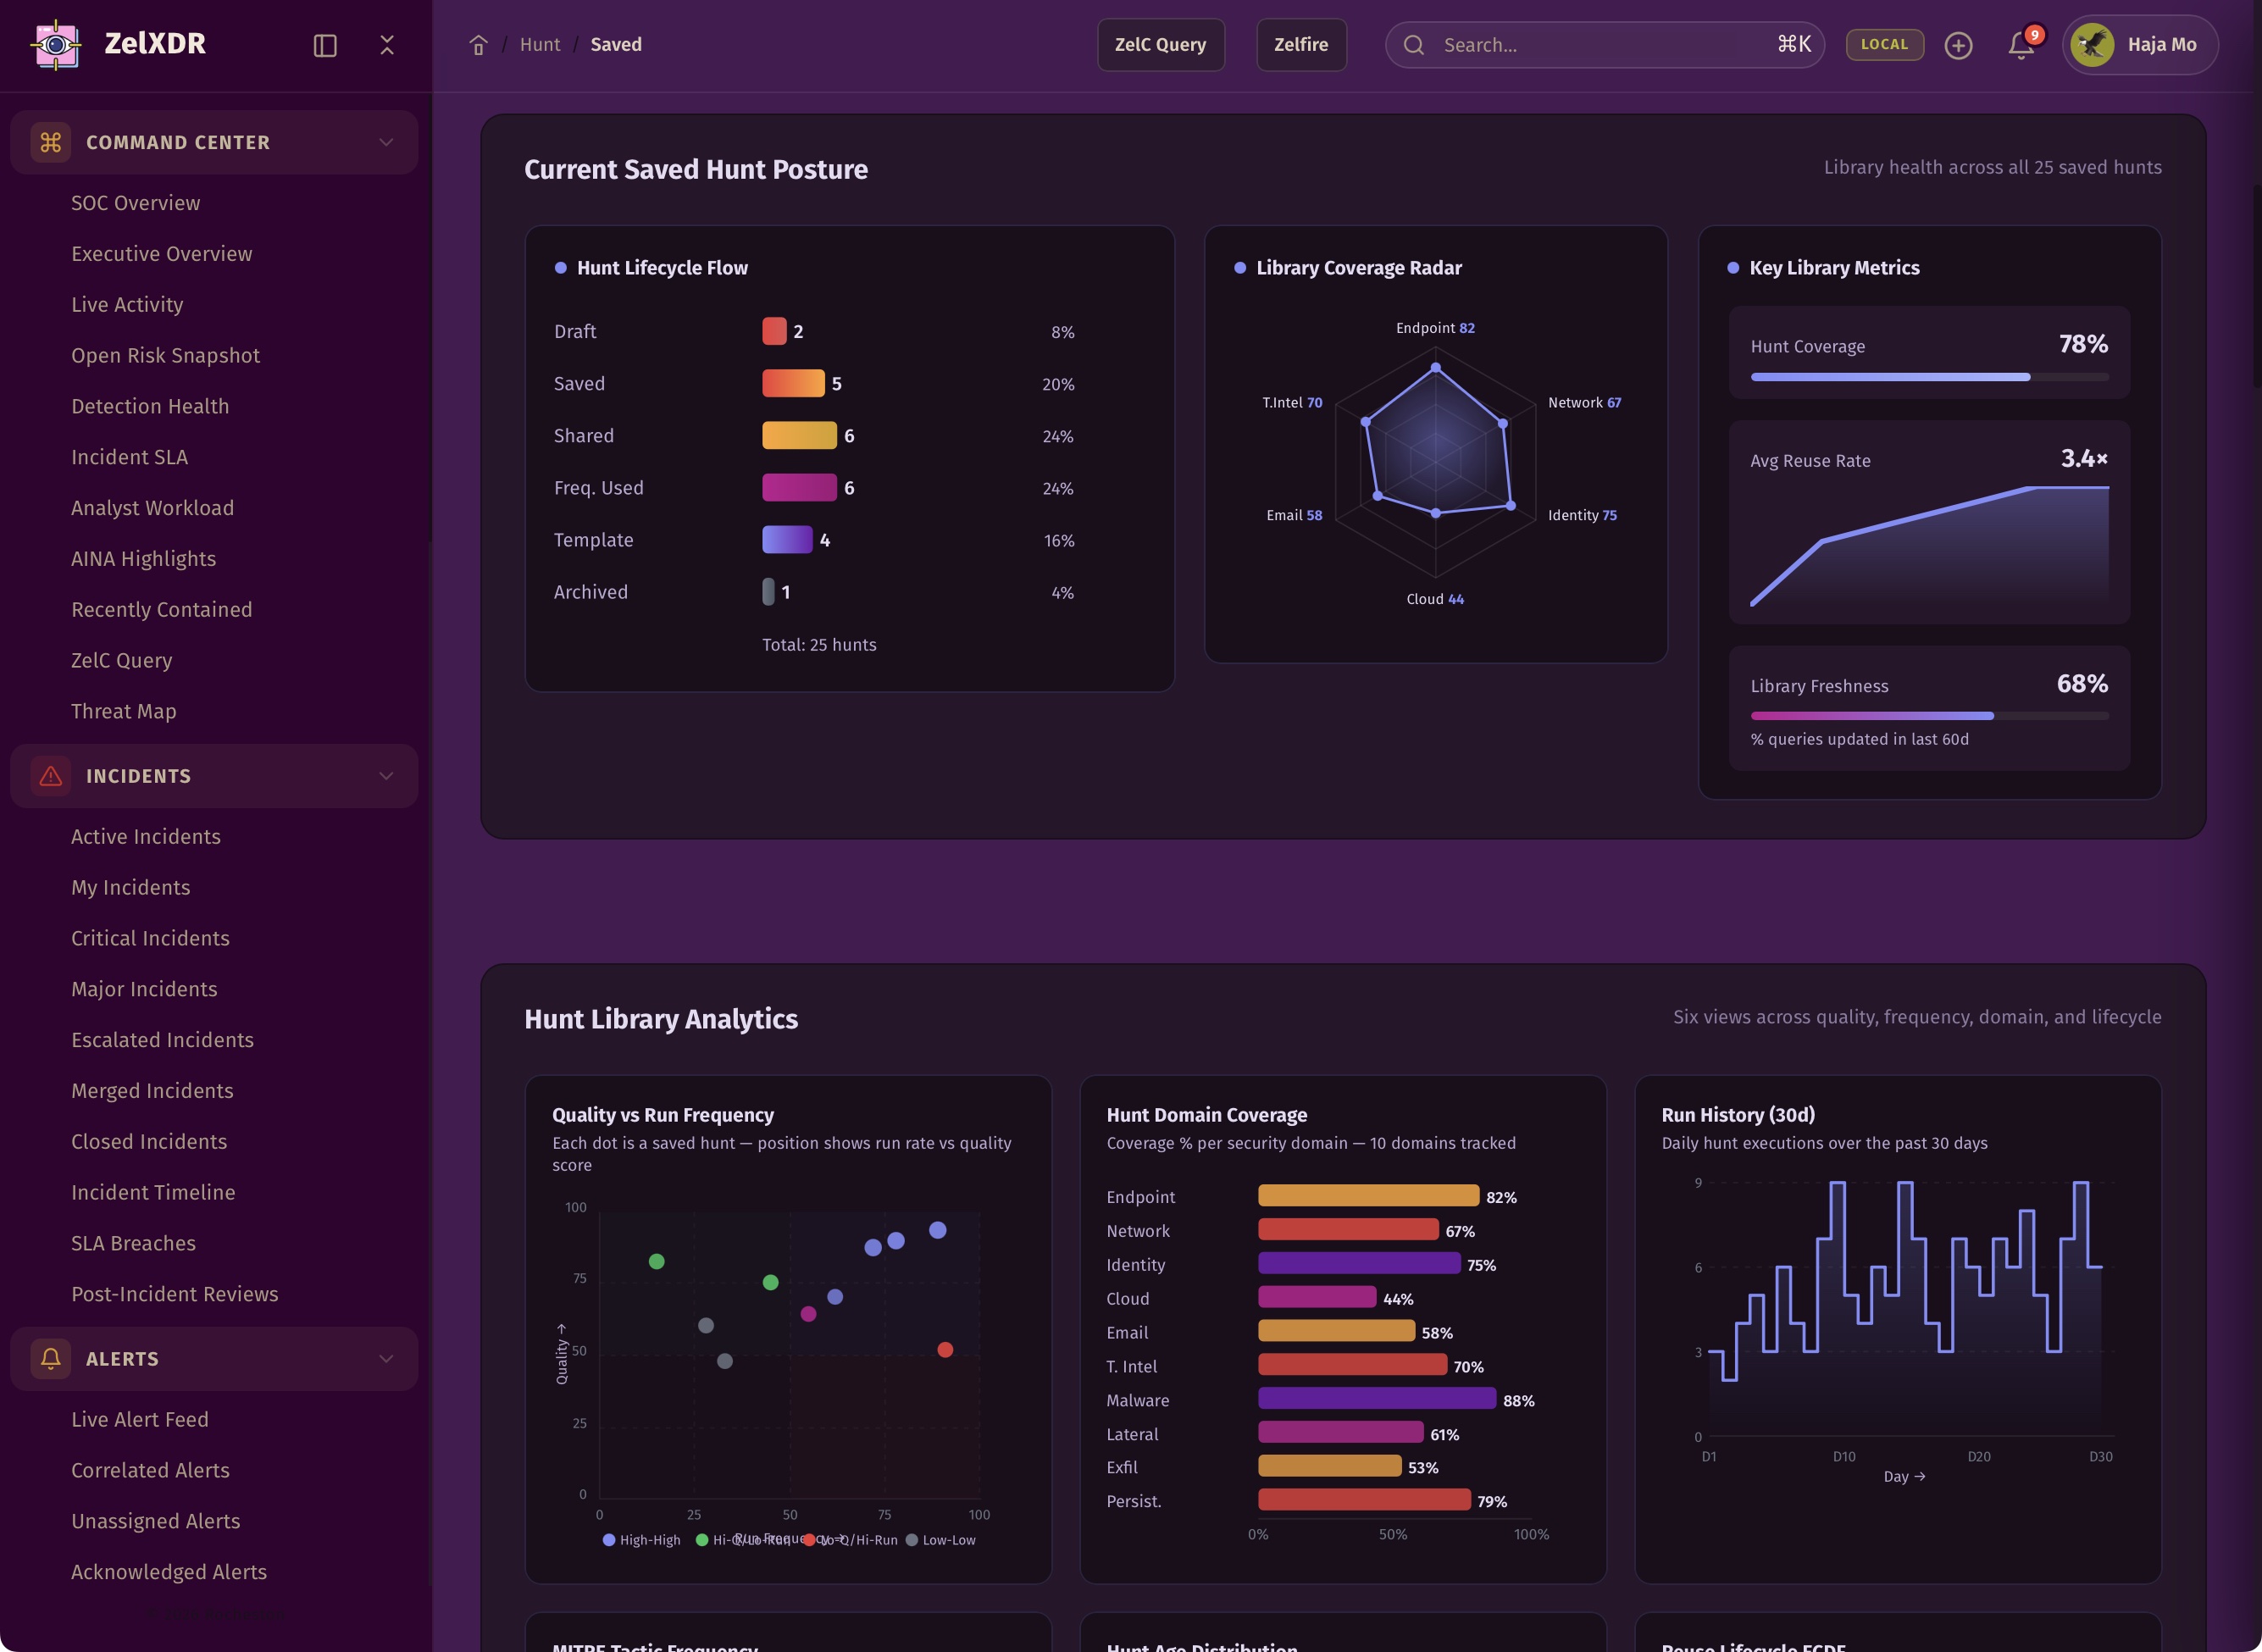
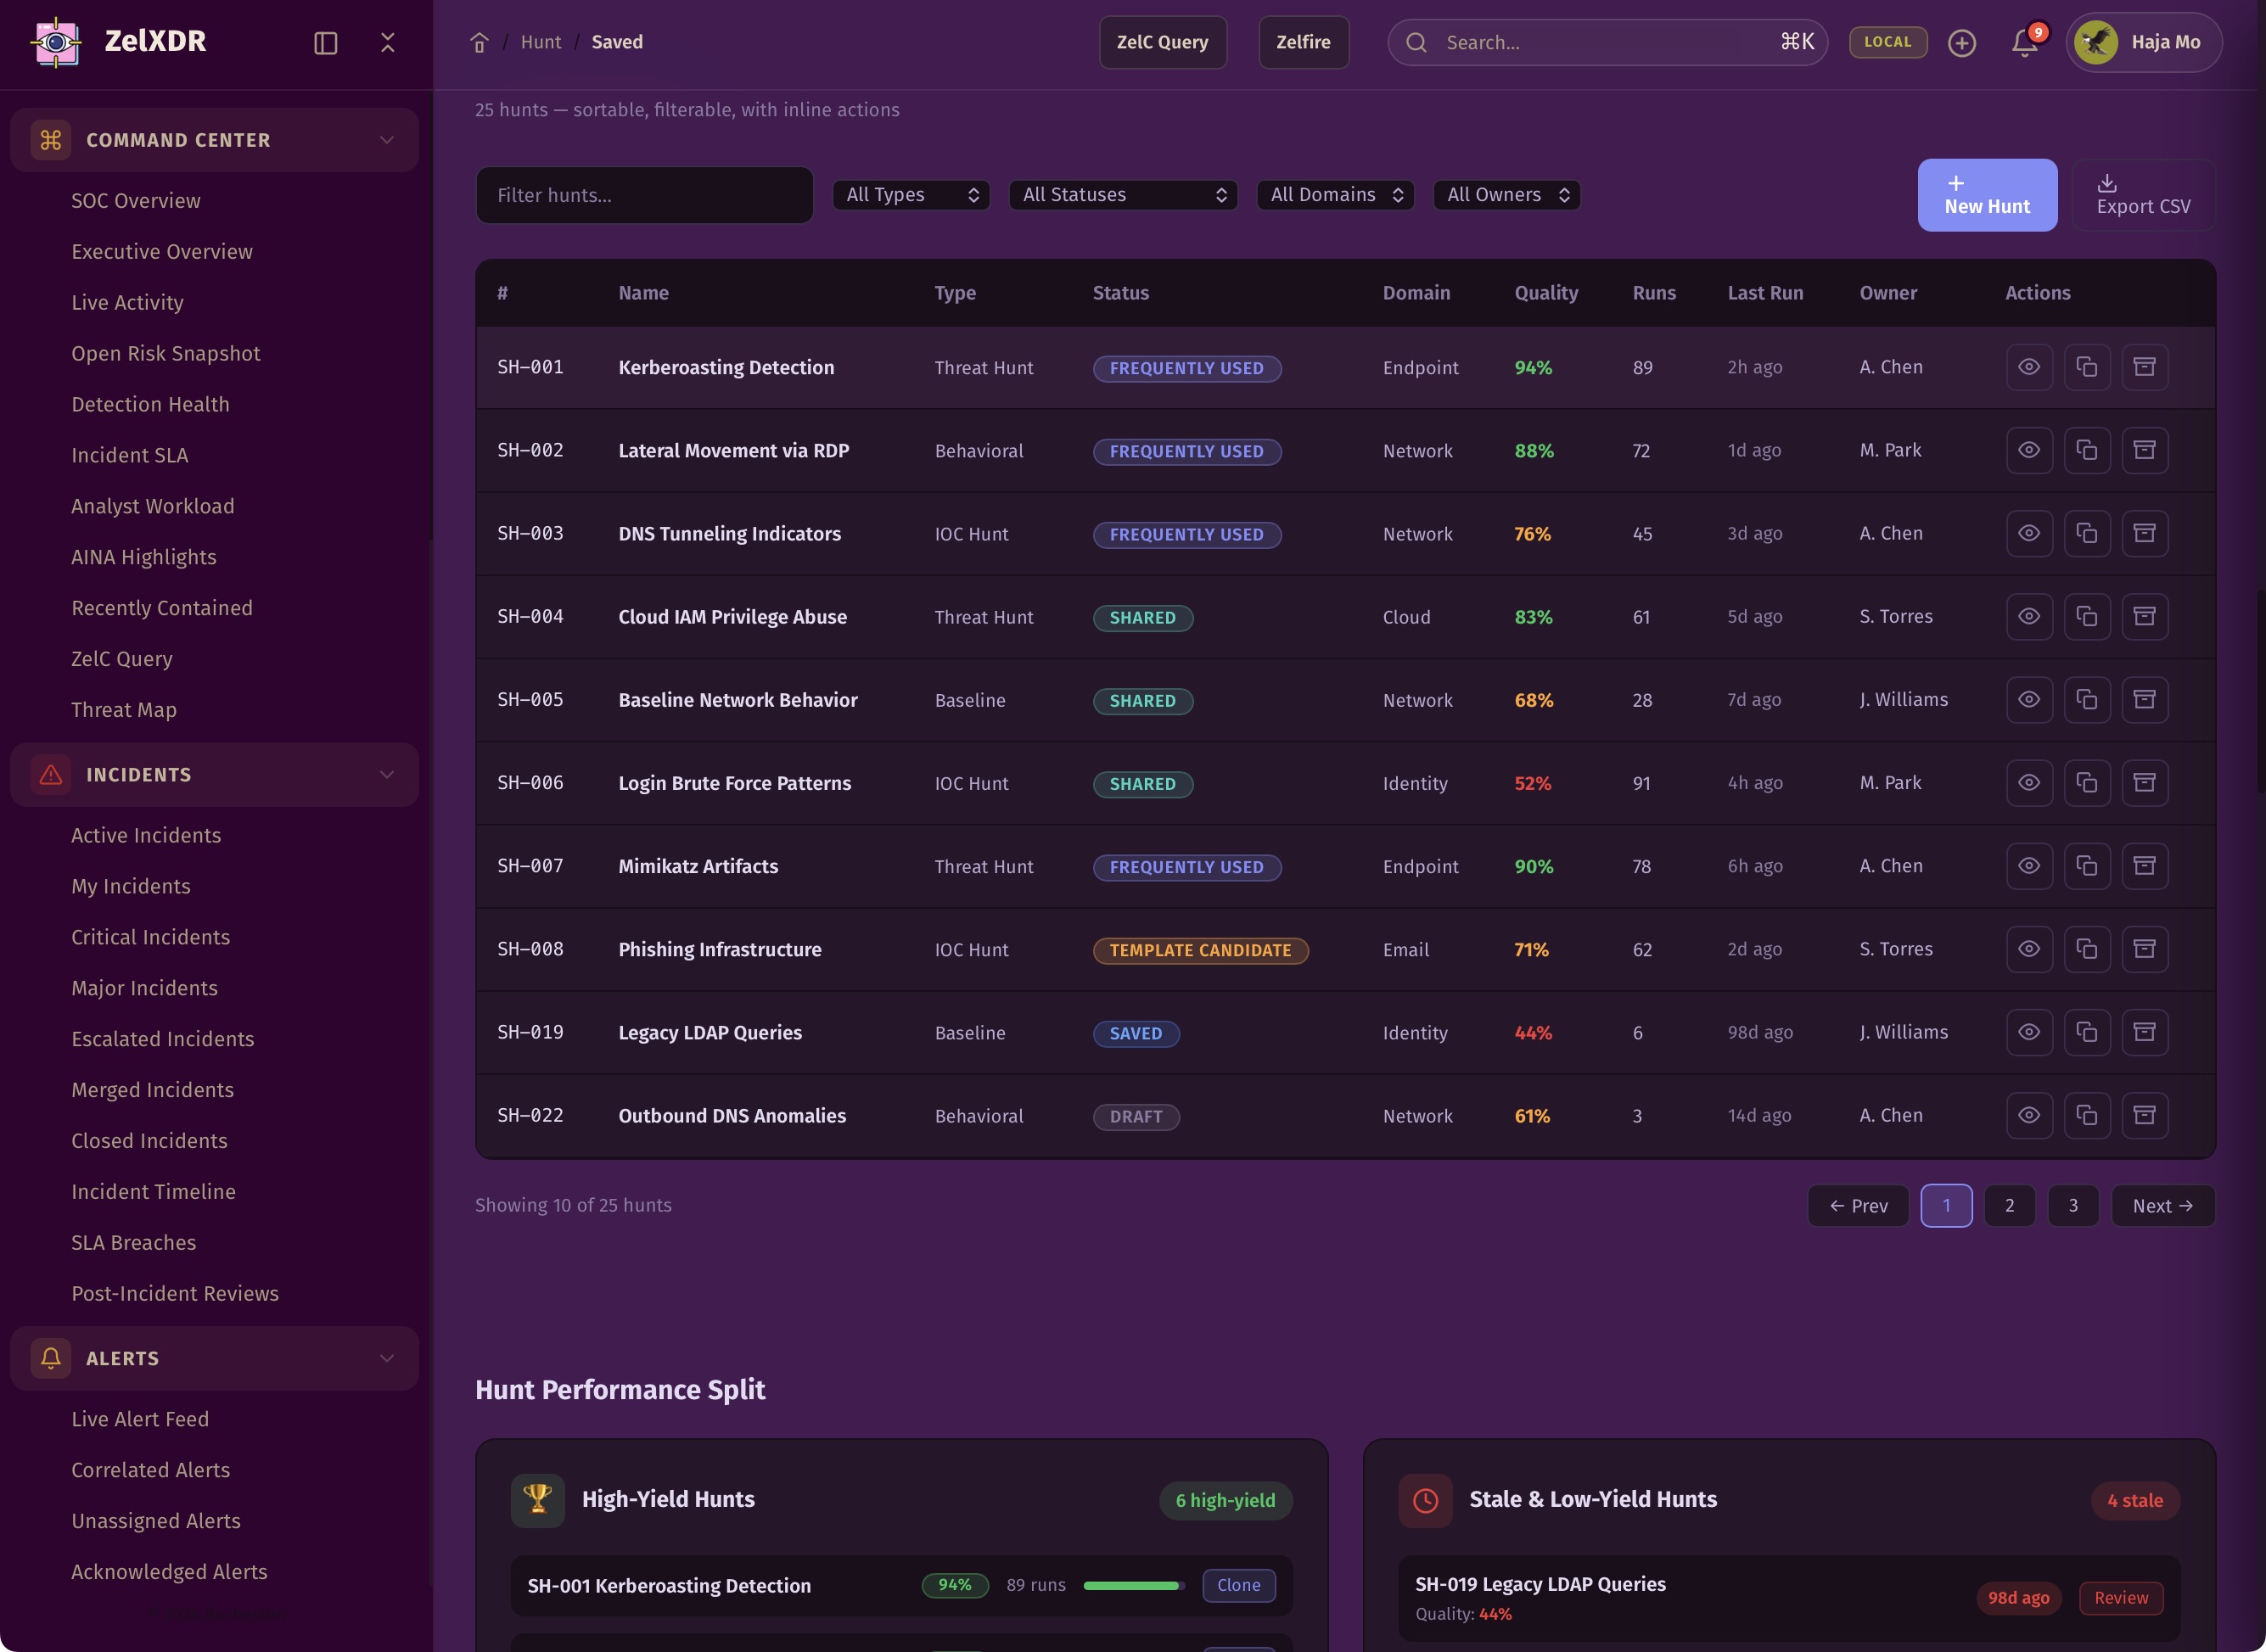
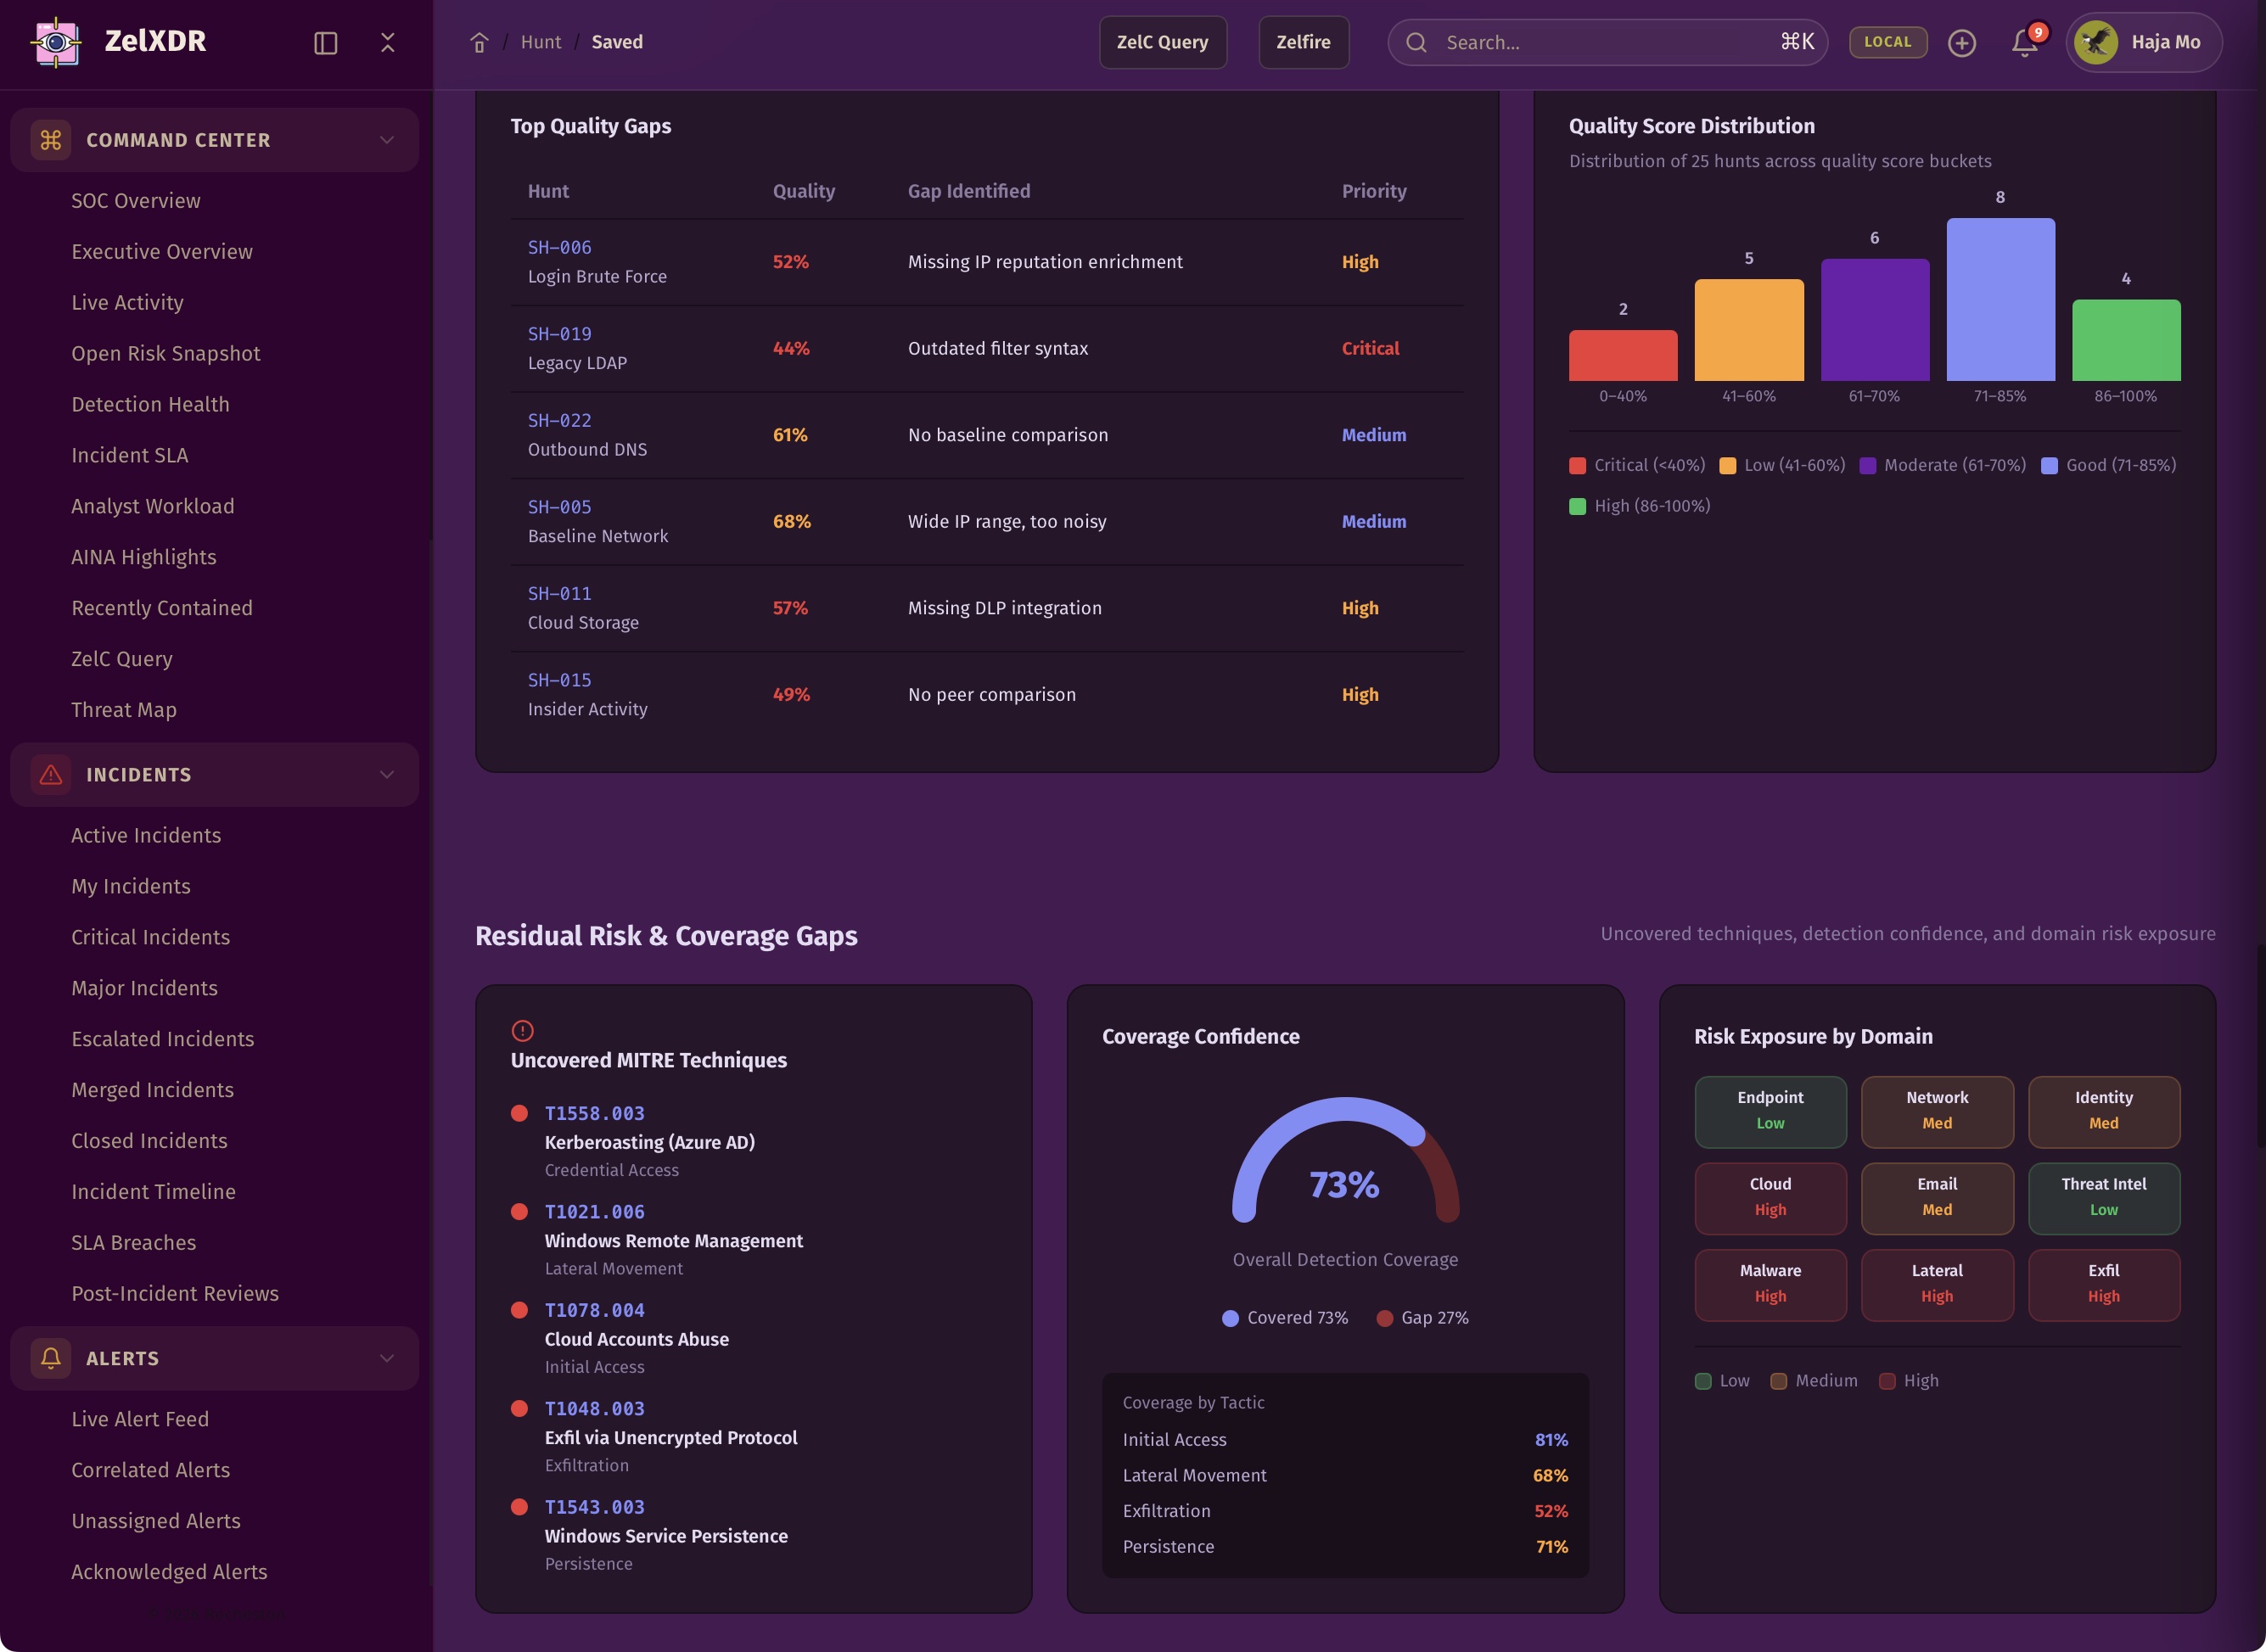
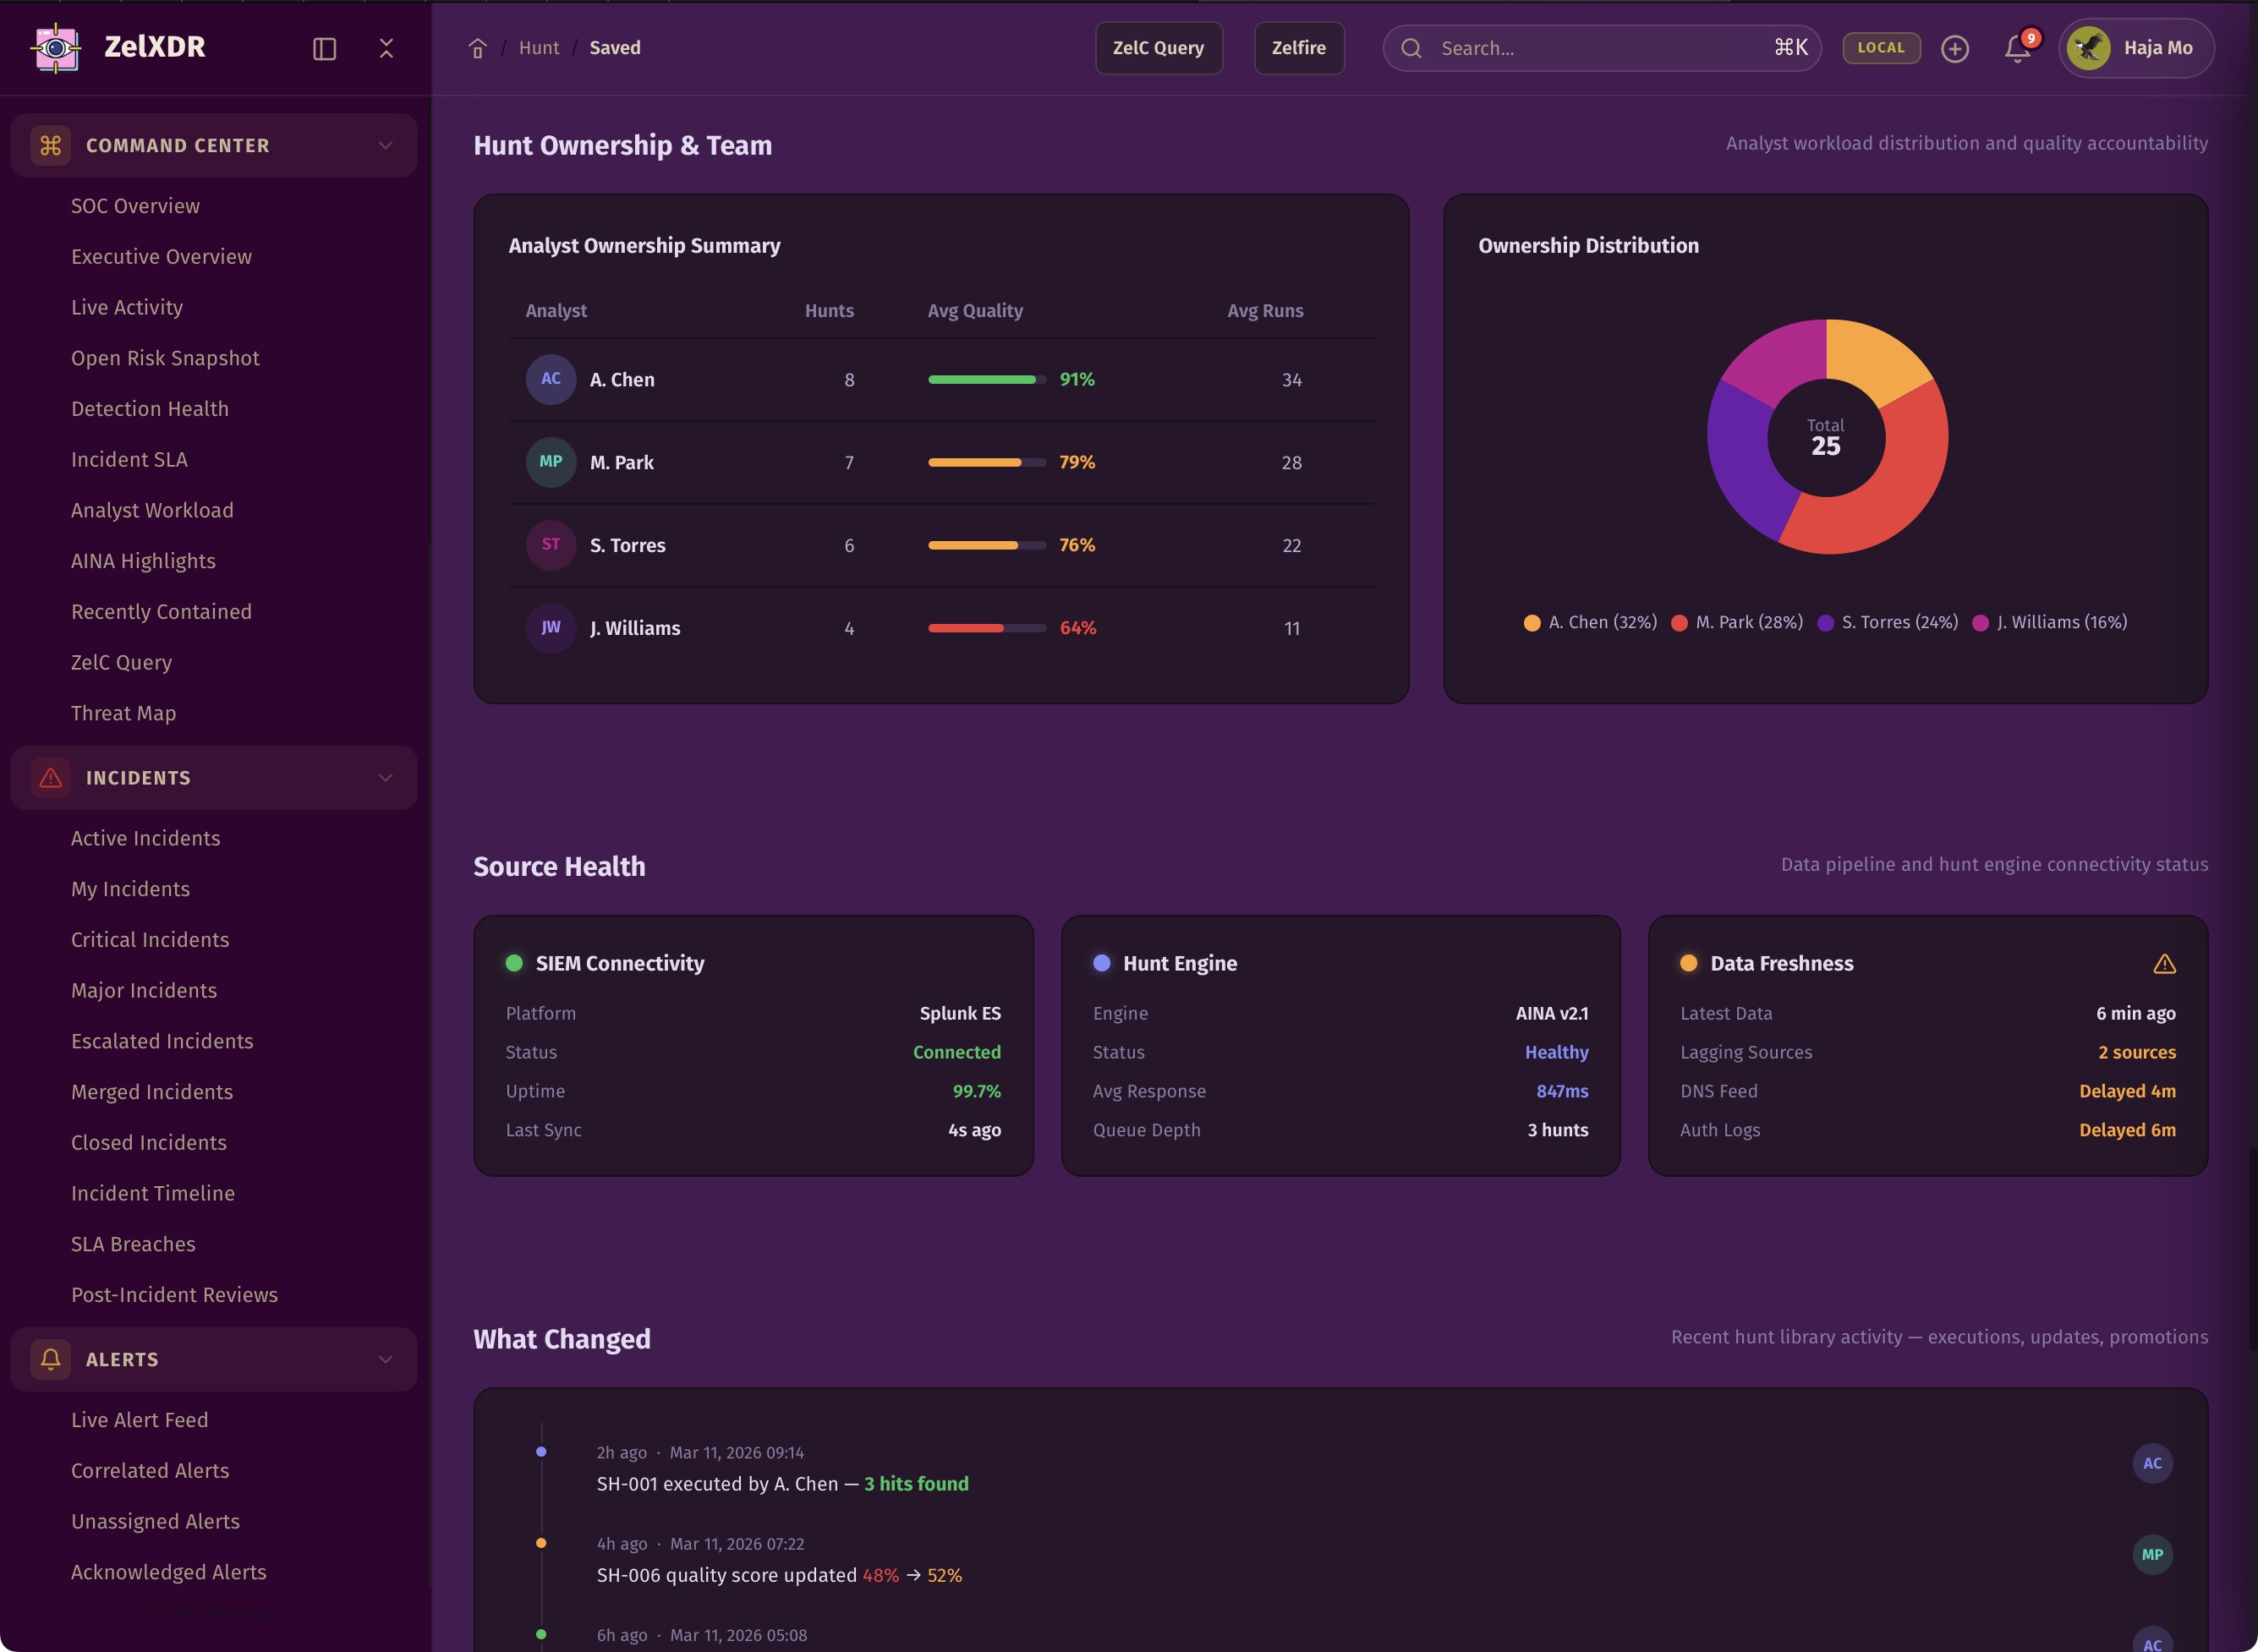
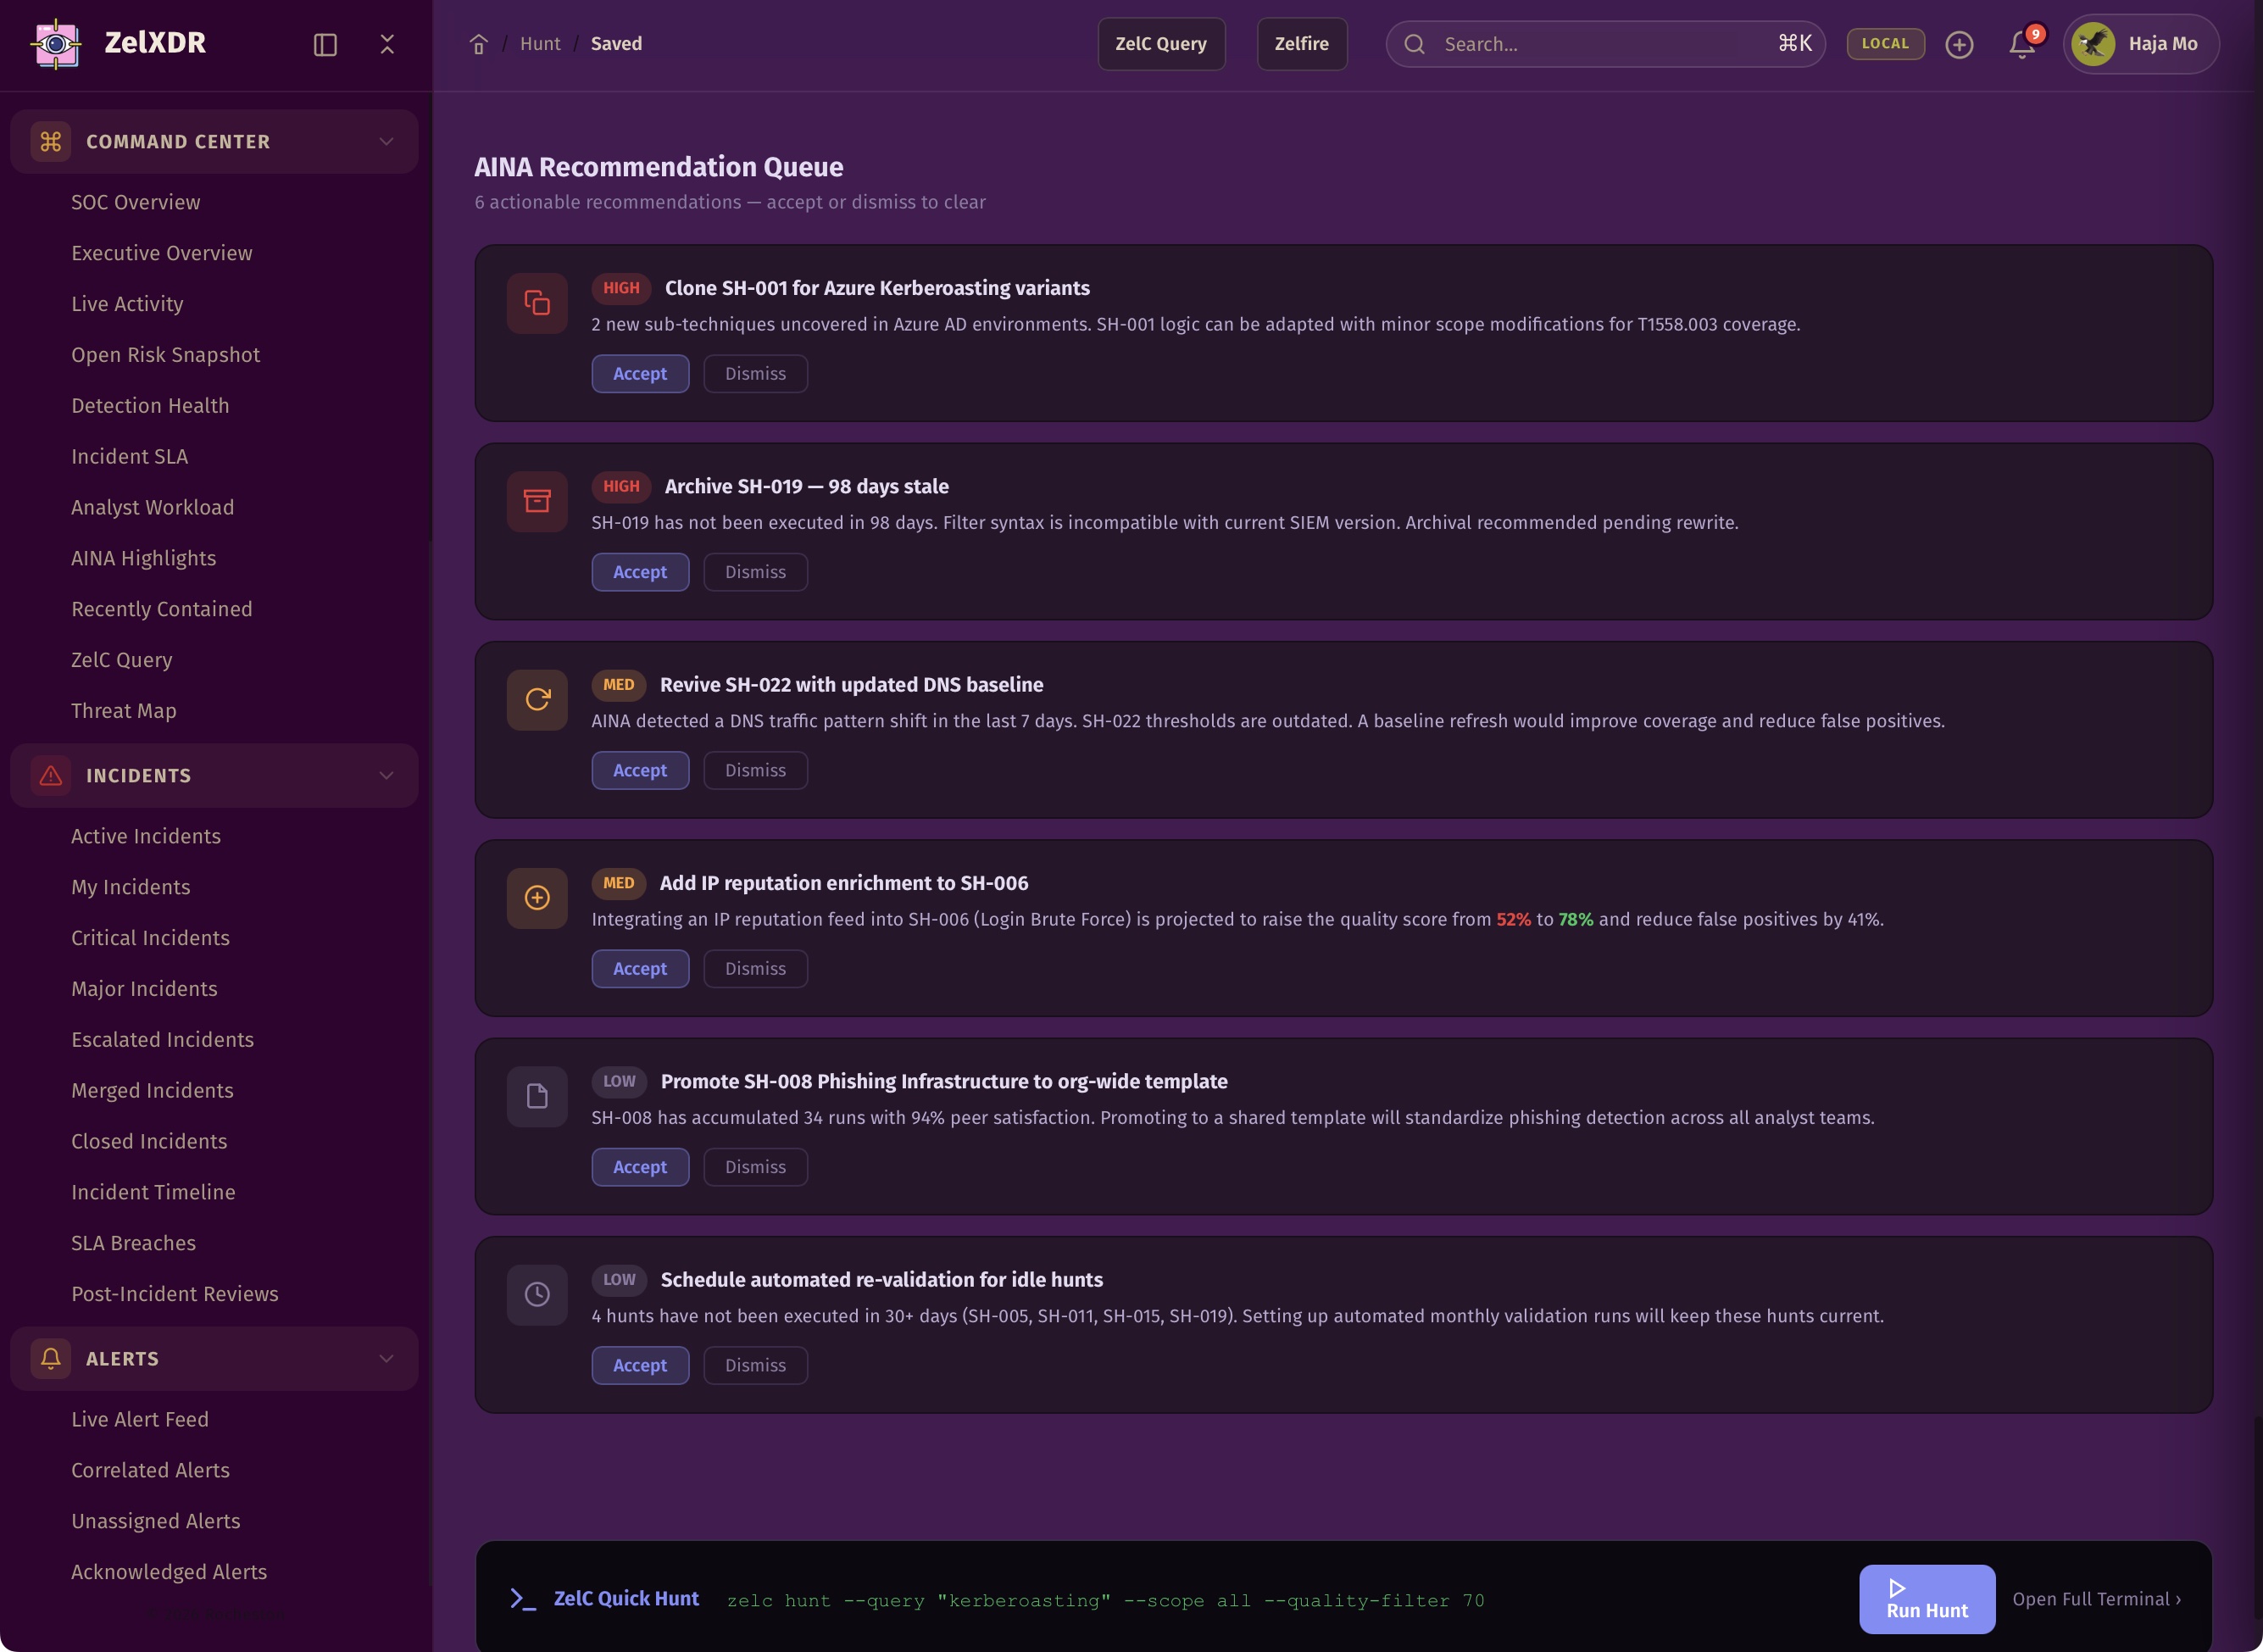
ZelXDR lets teams save high-value hunt logic for reuse, sharing, and scaling. This creates a hunt library that becomes smarter and more valuable over time.
Every strong hunt should become reusable knowledge.
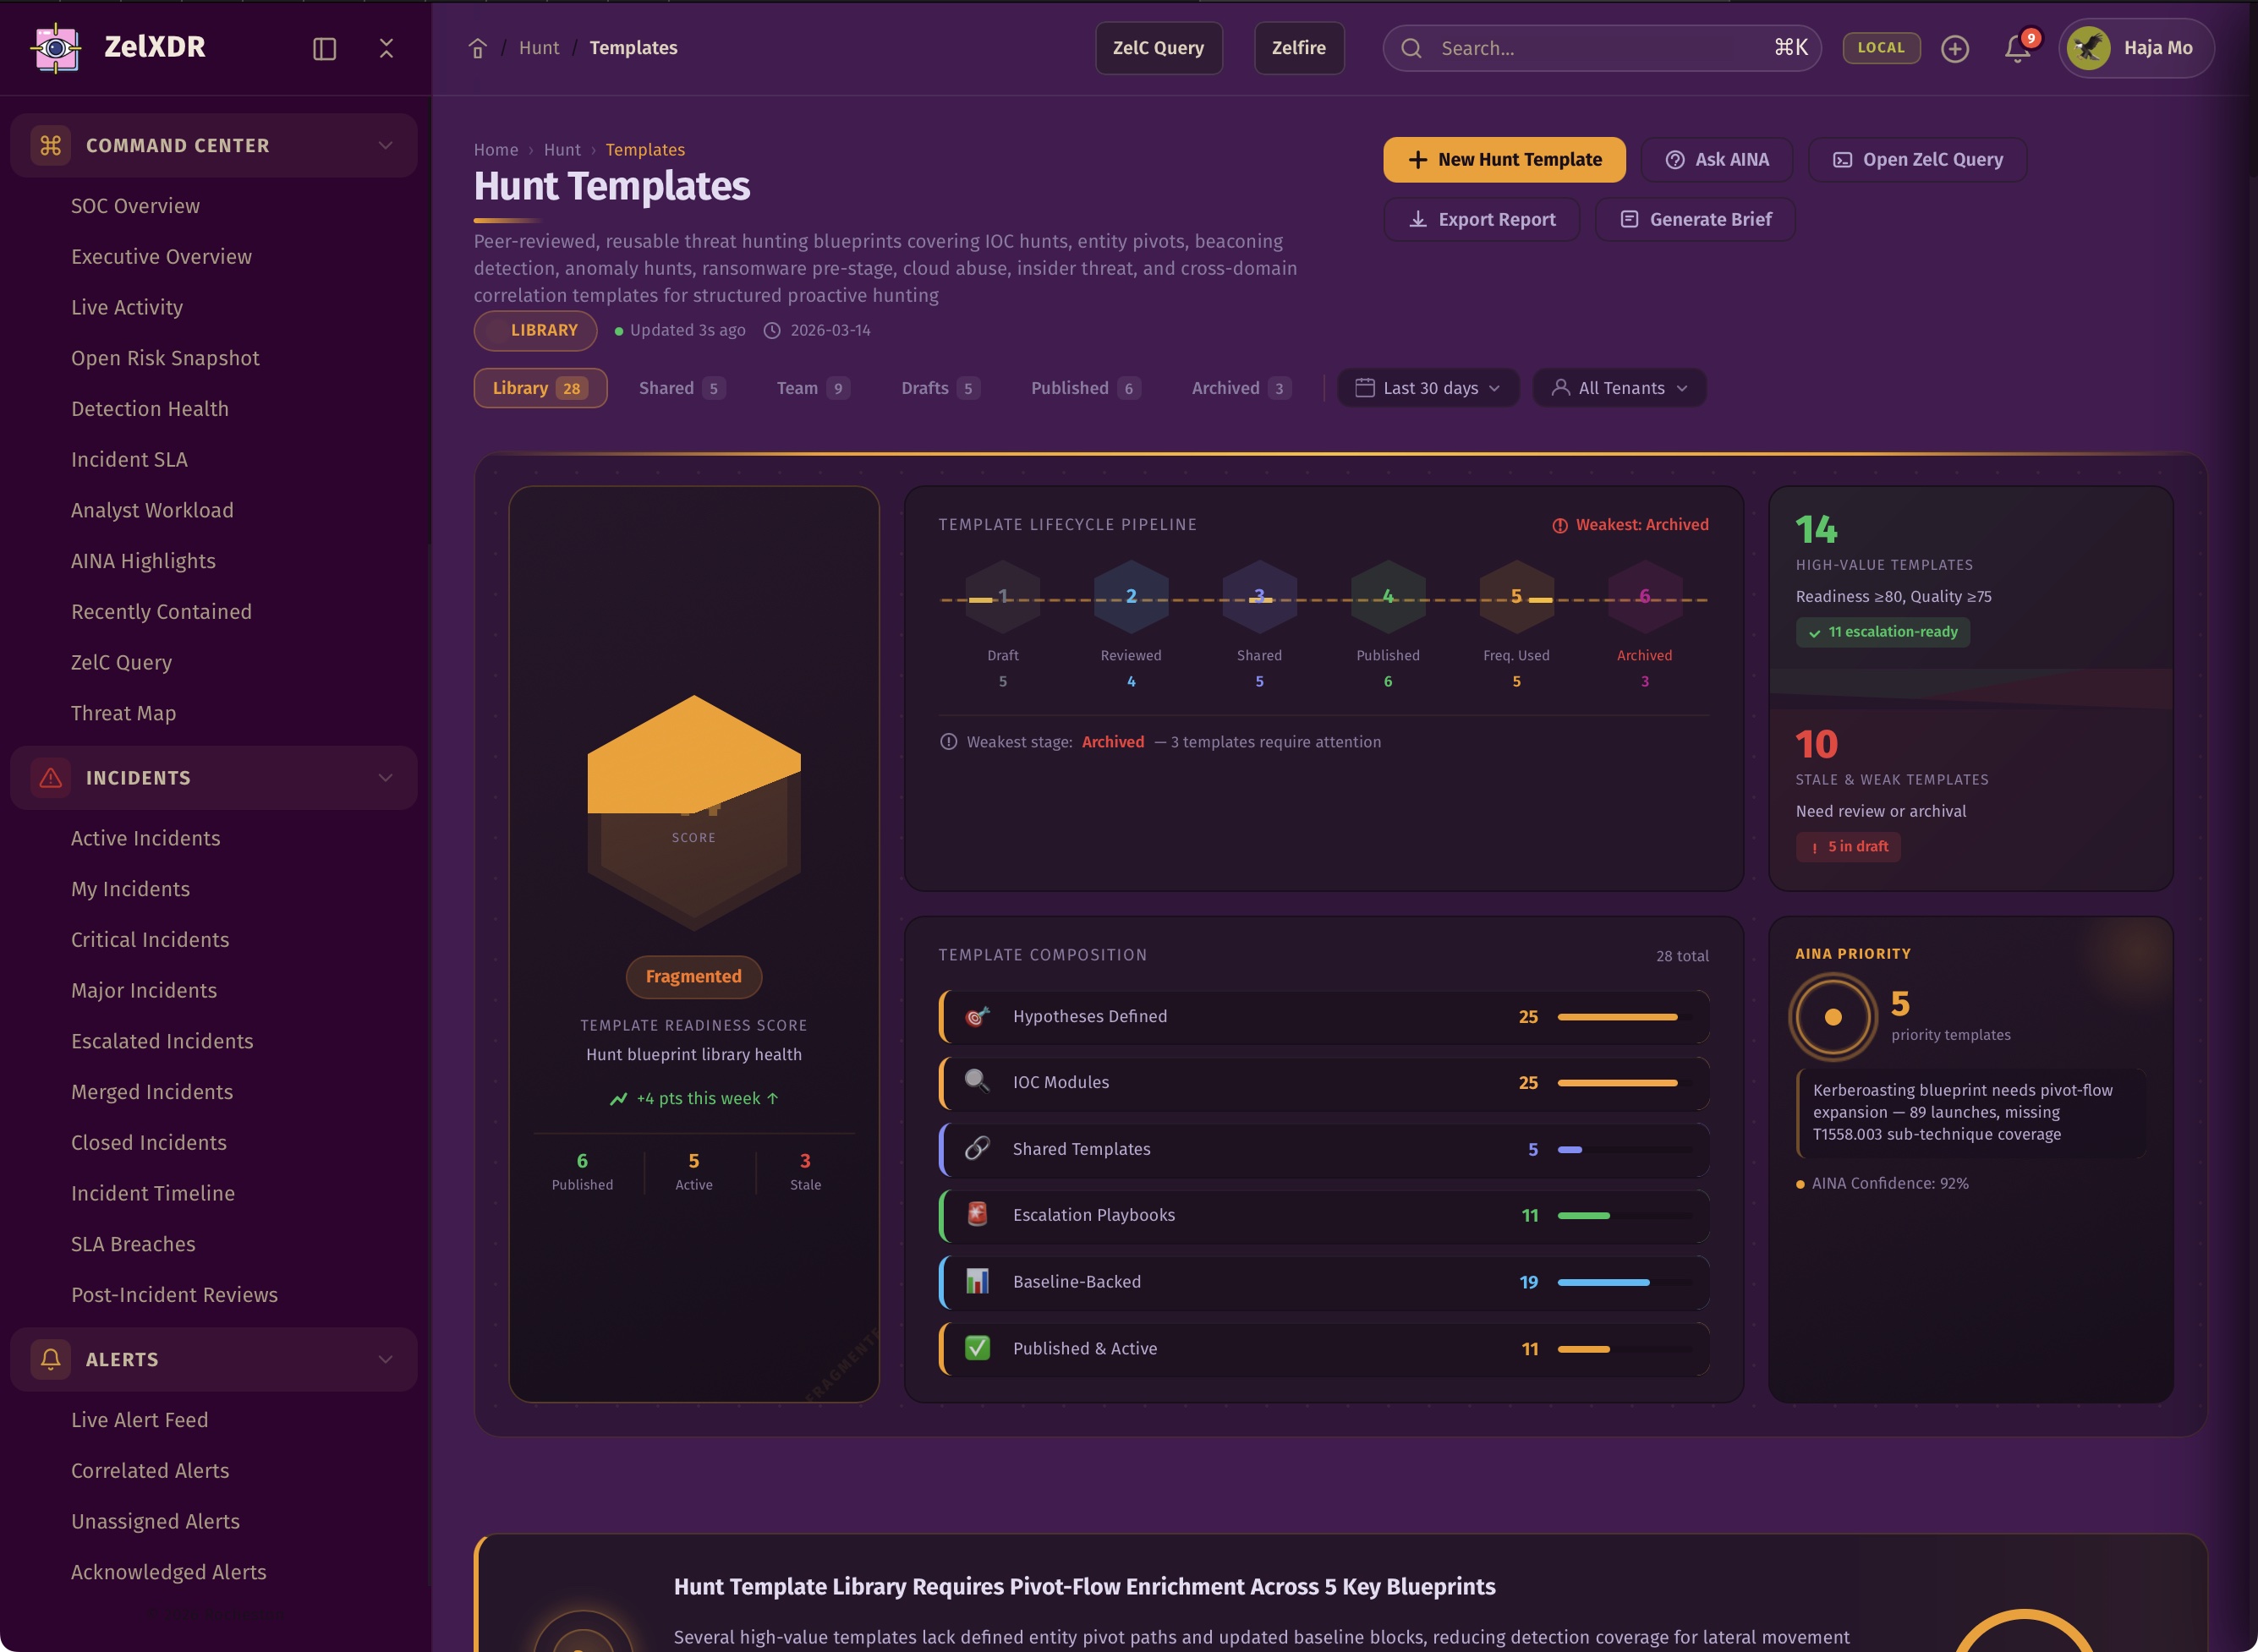
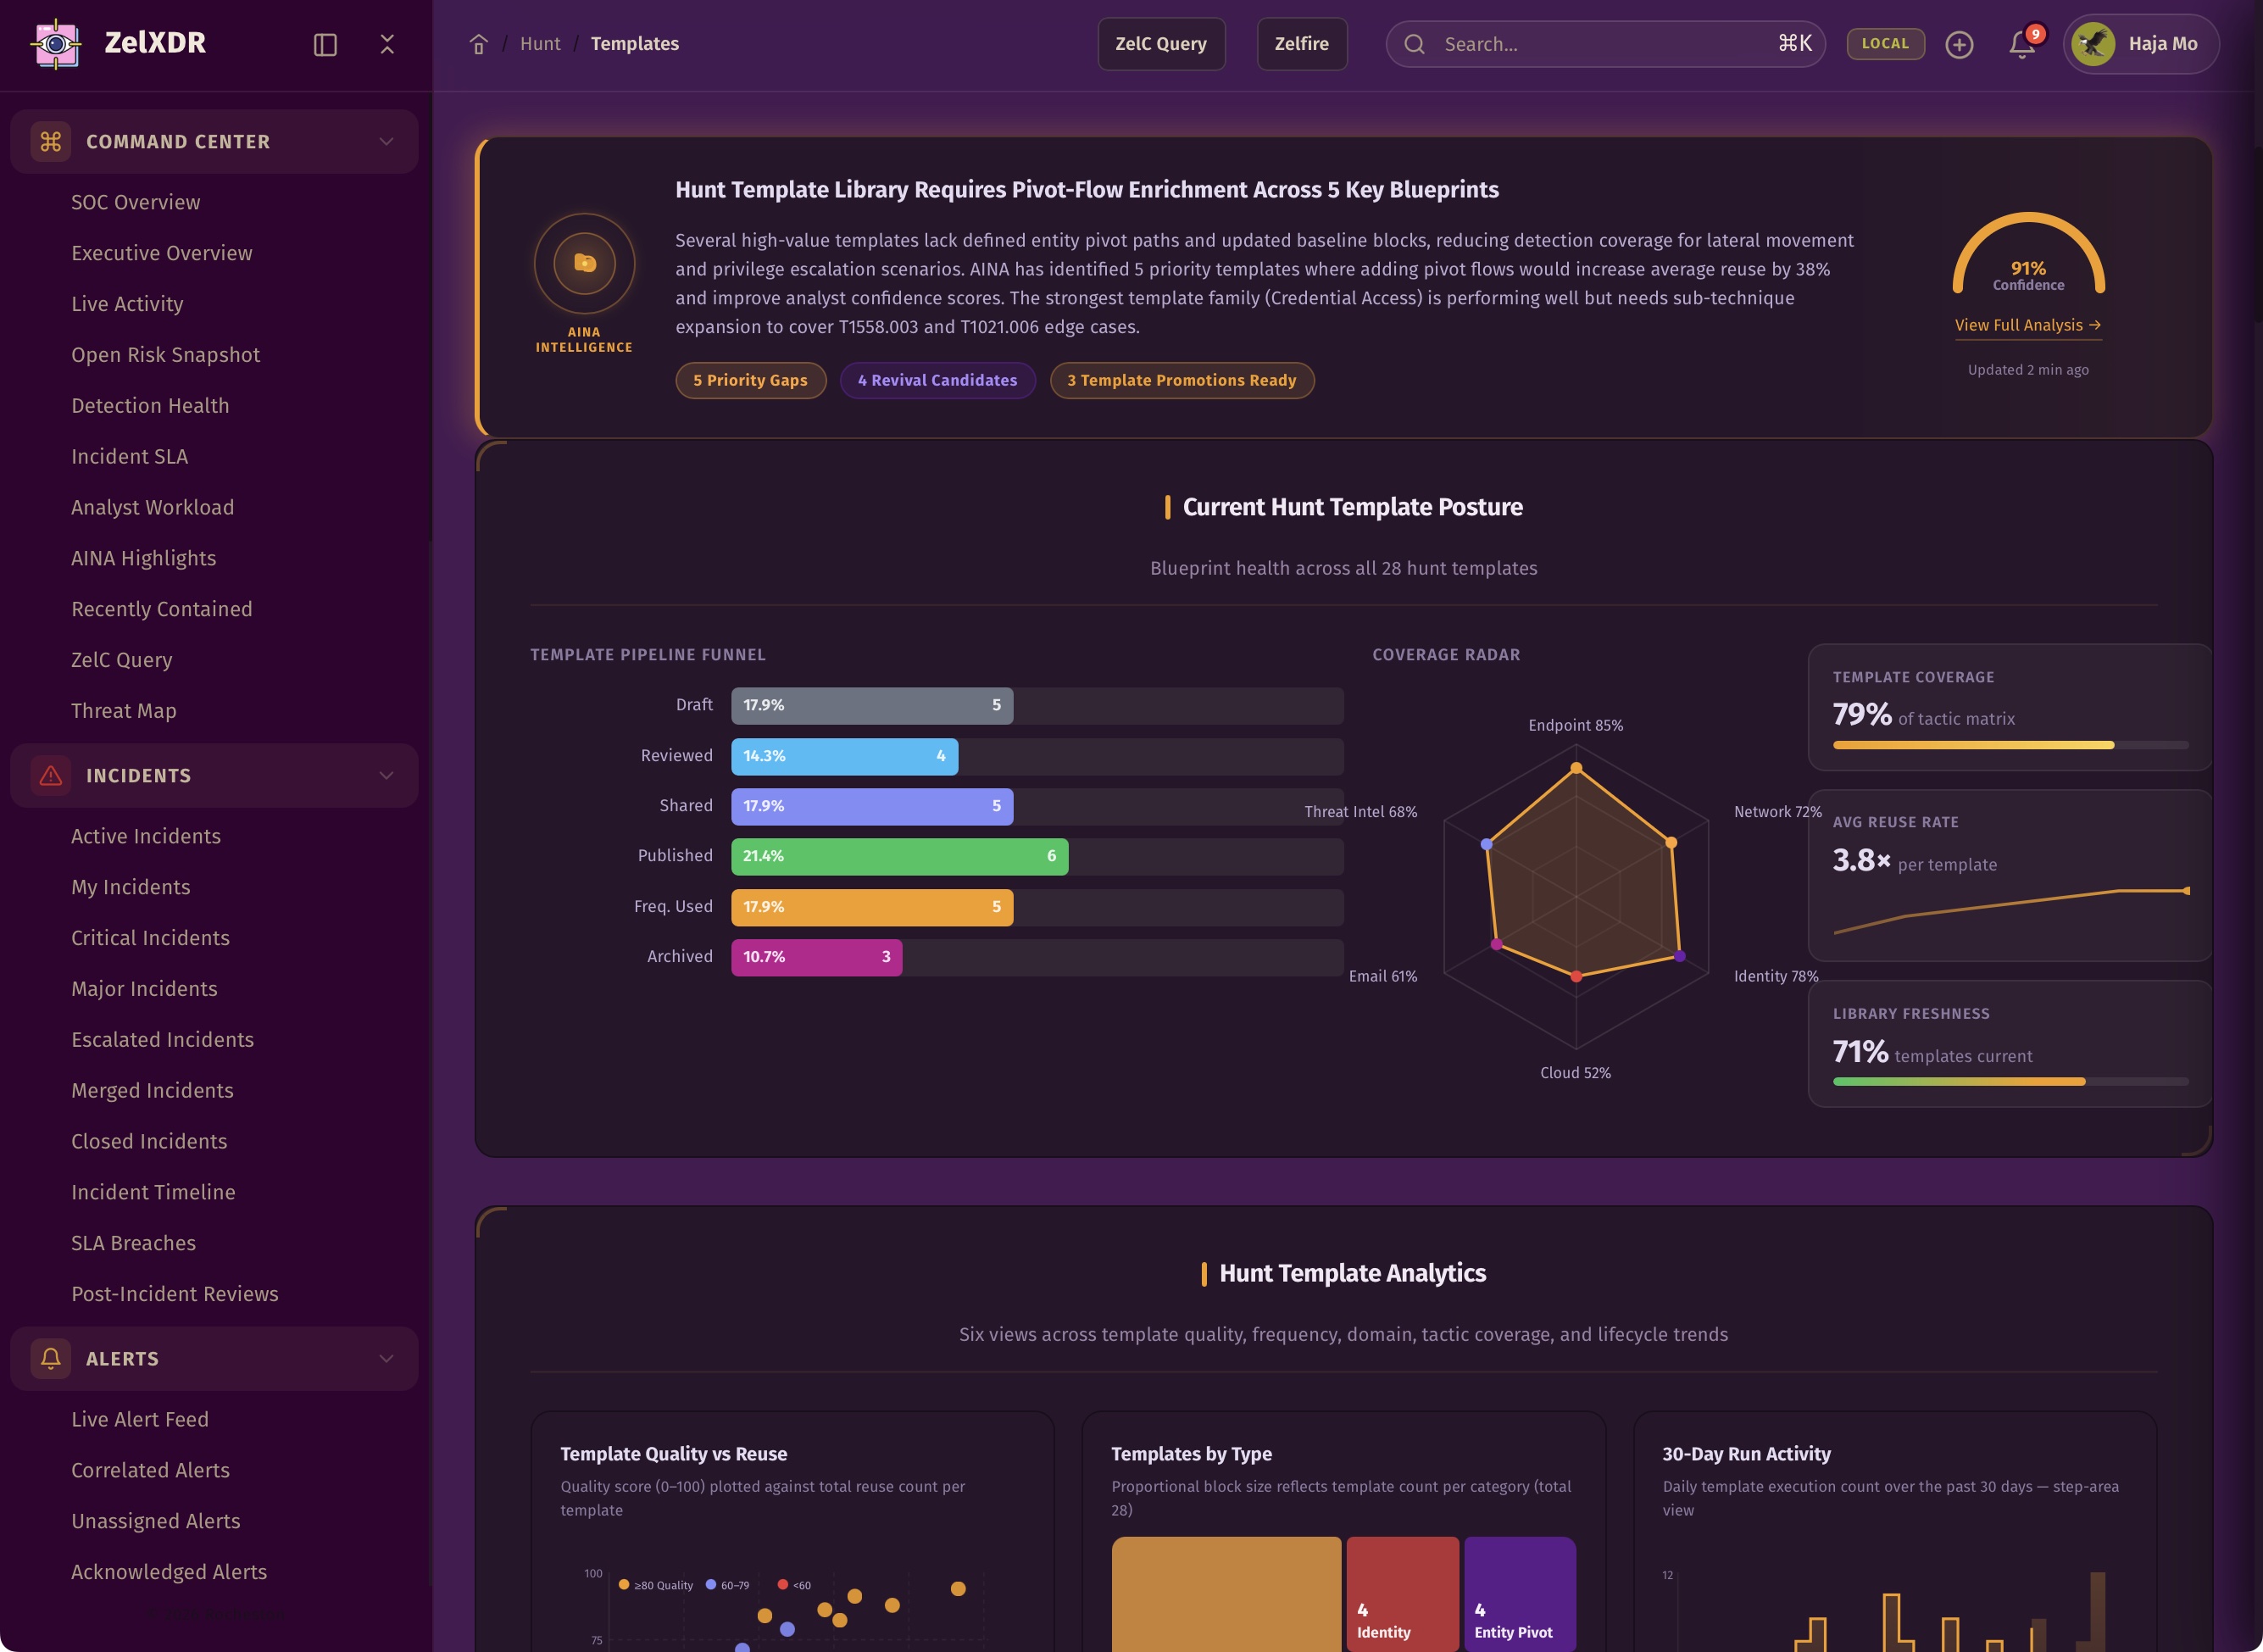
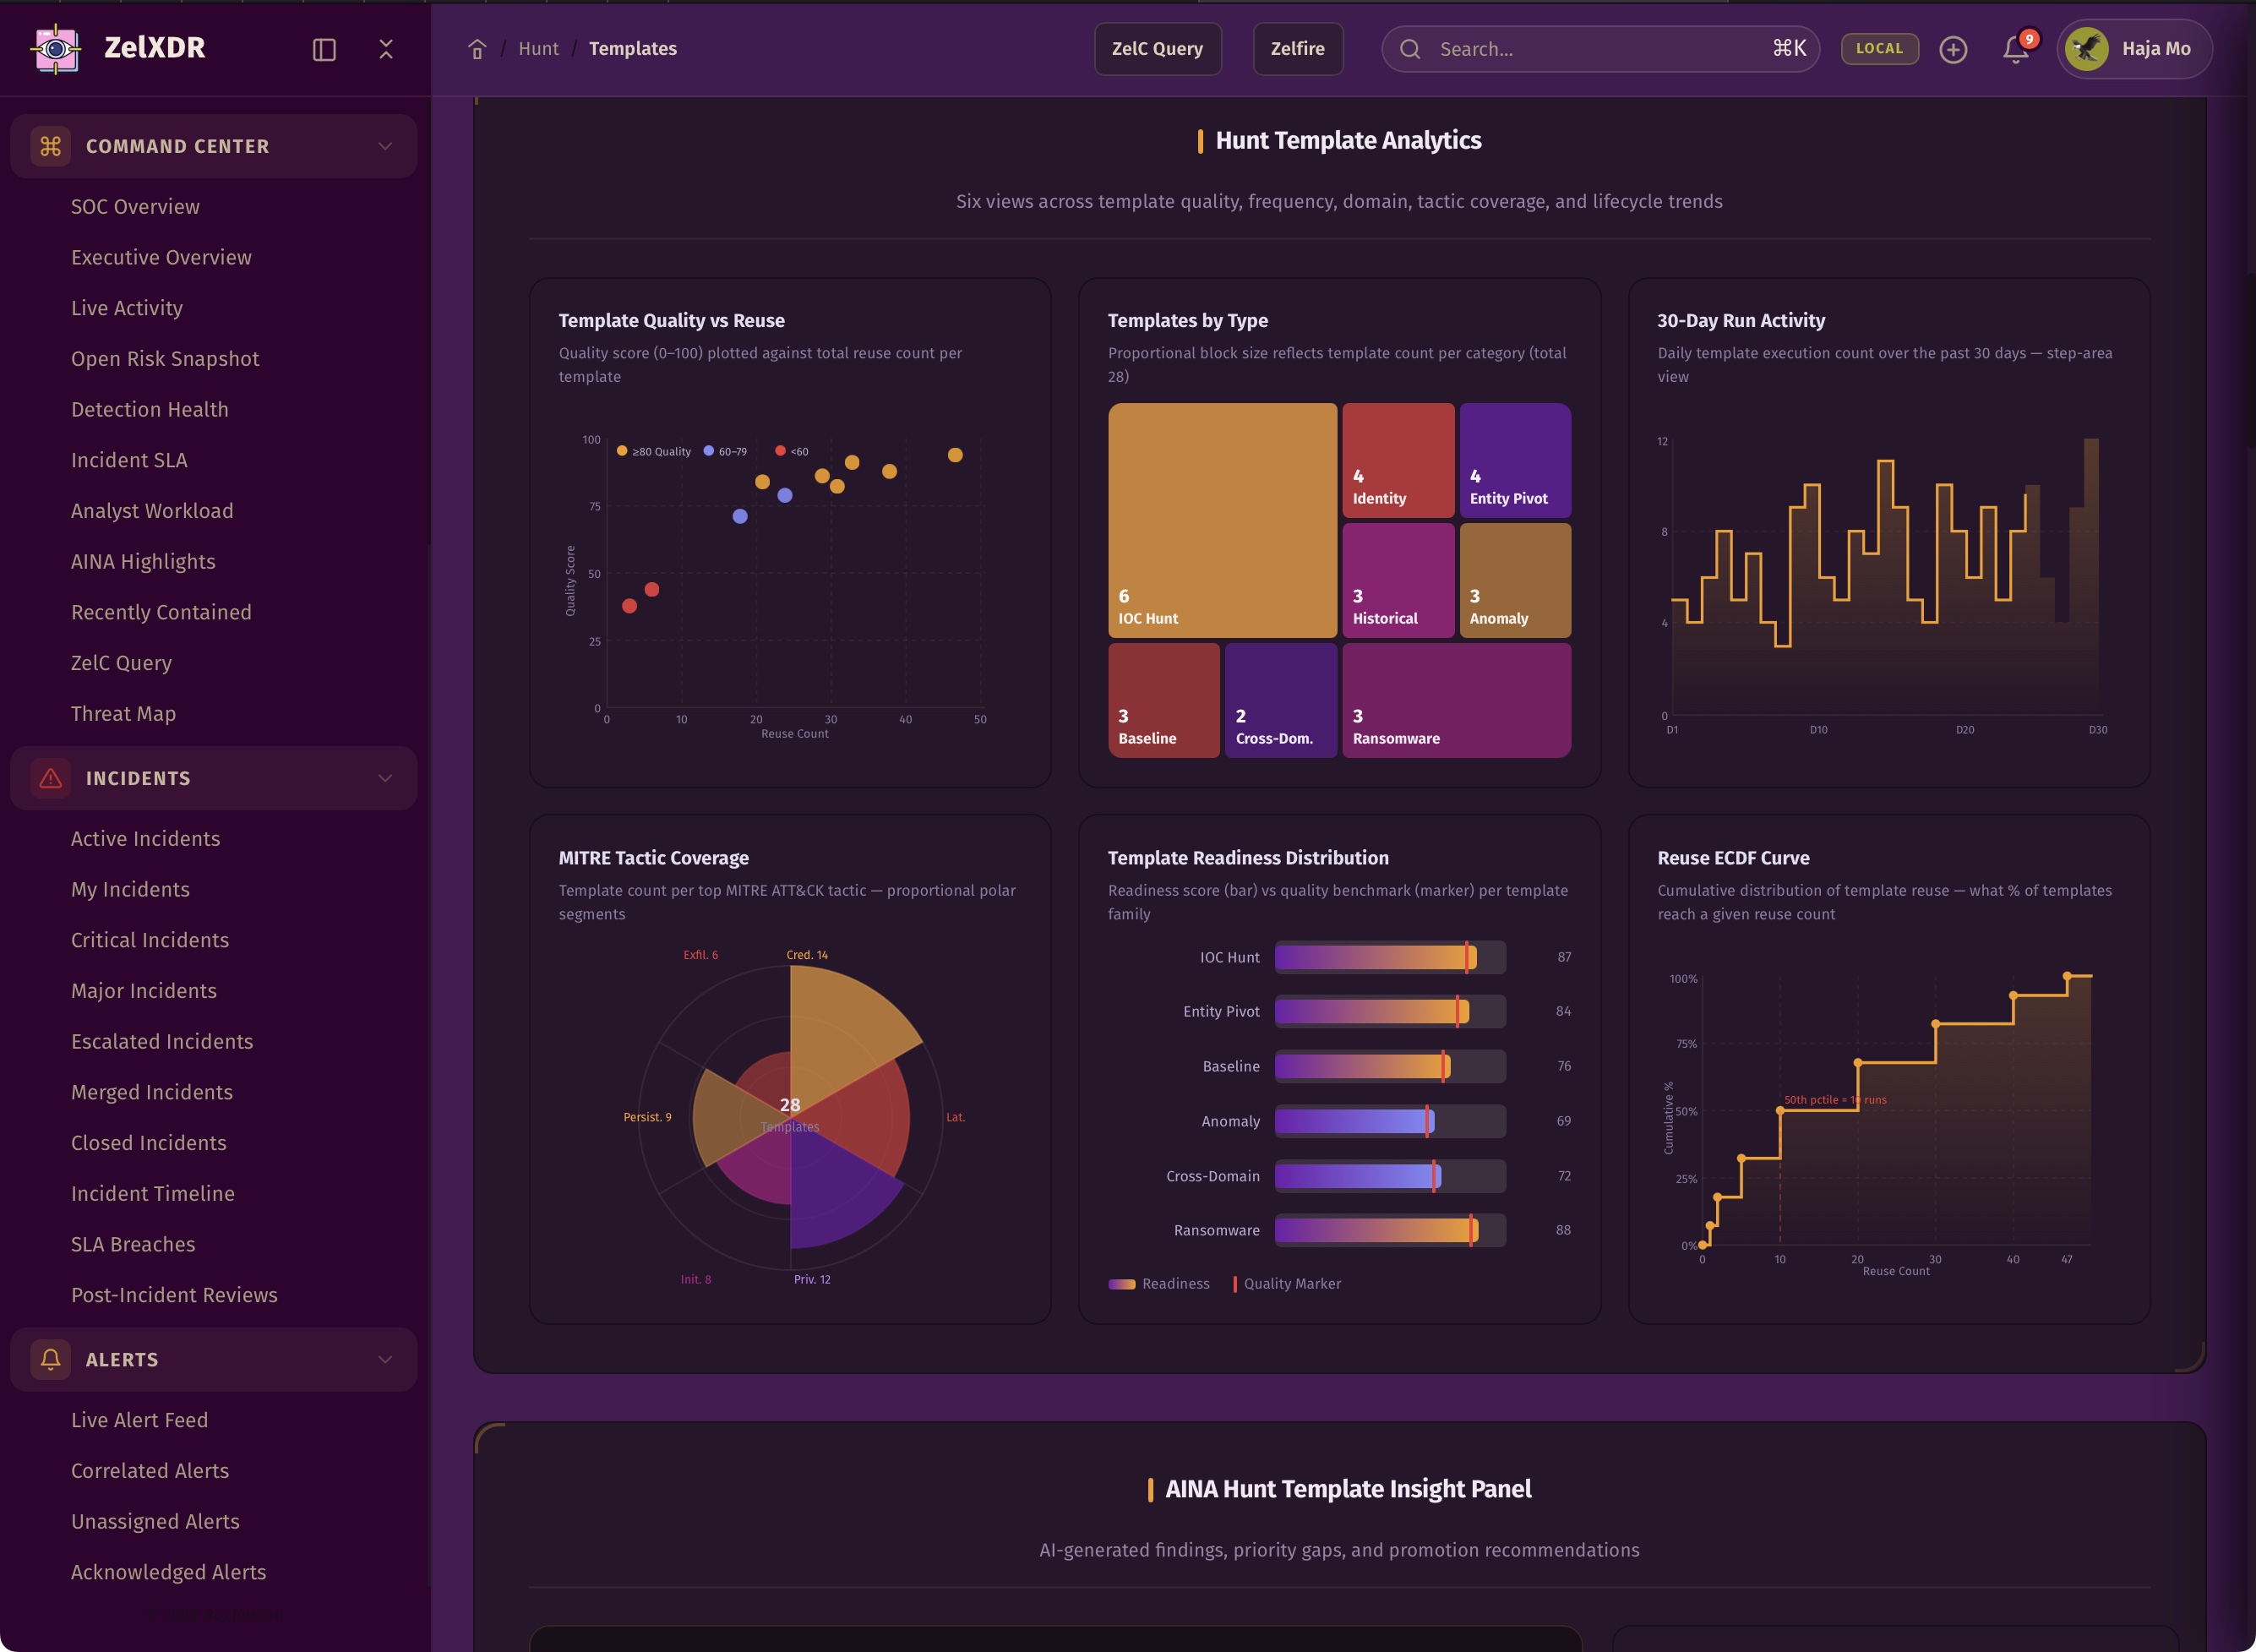
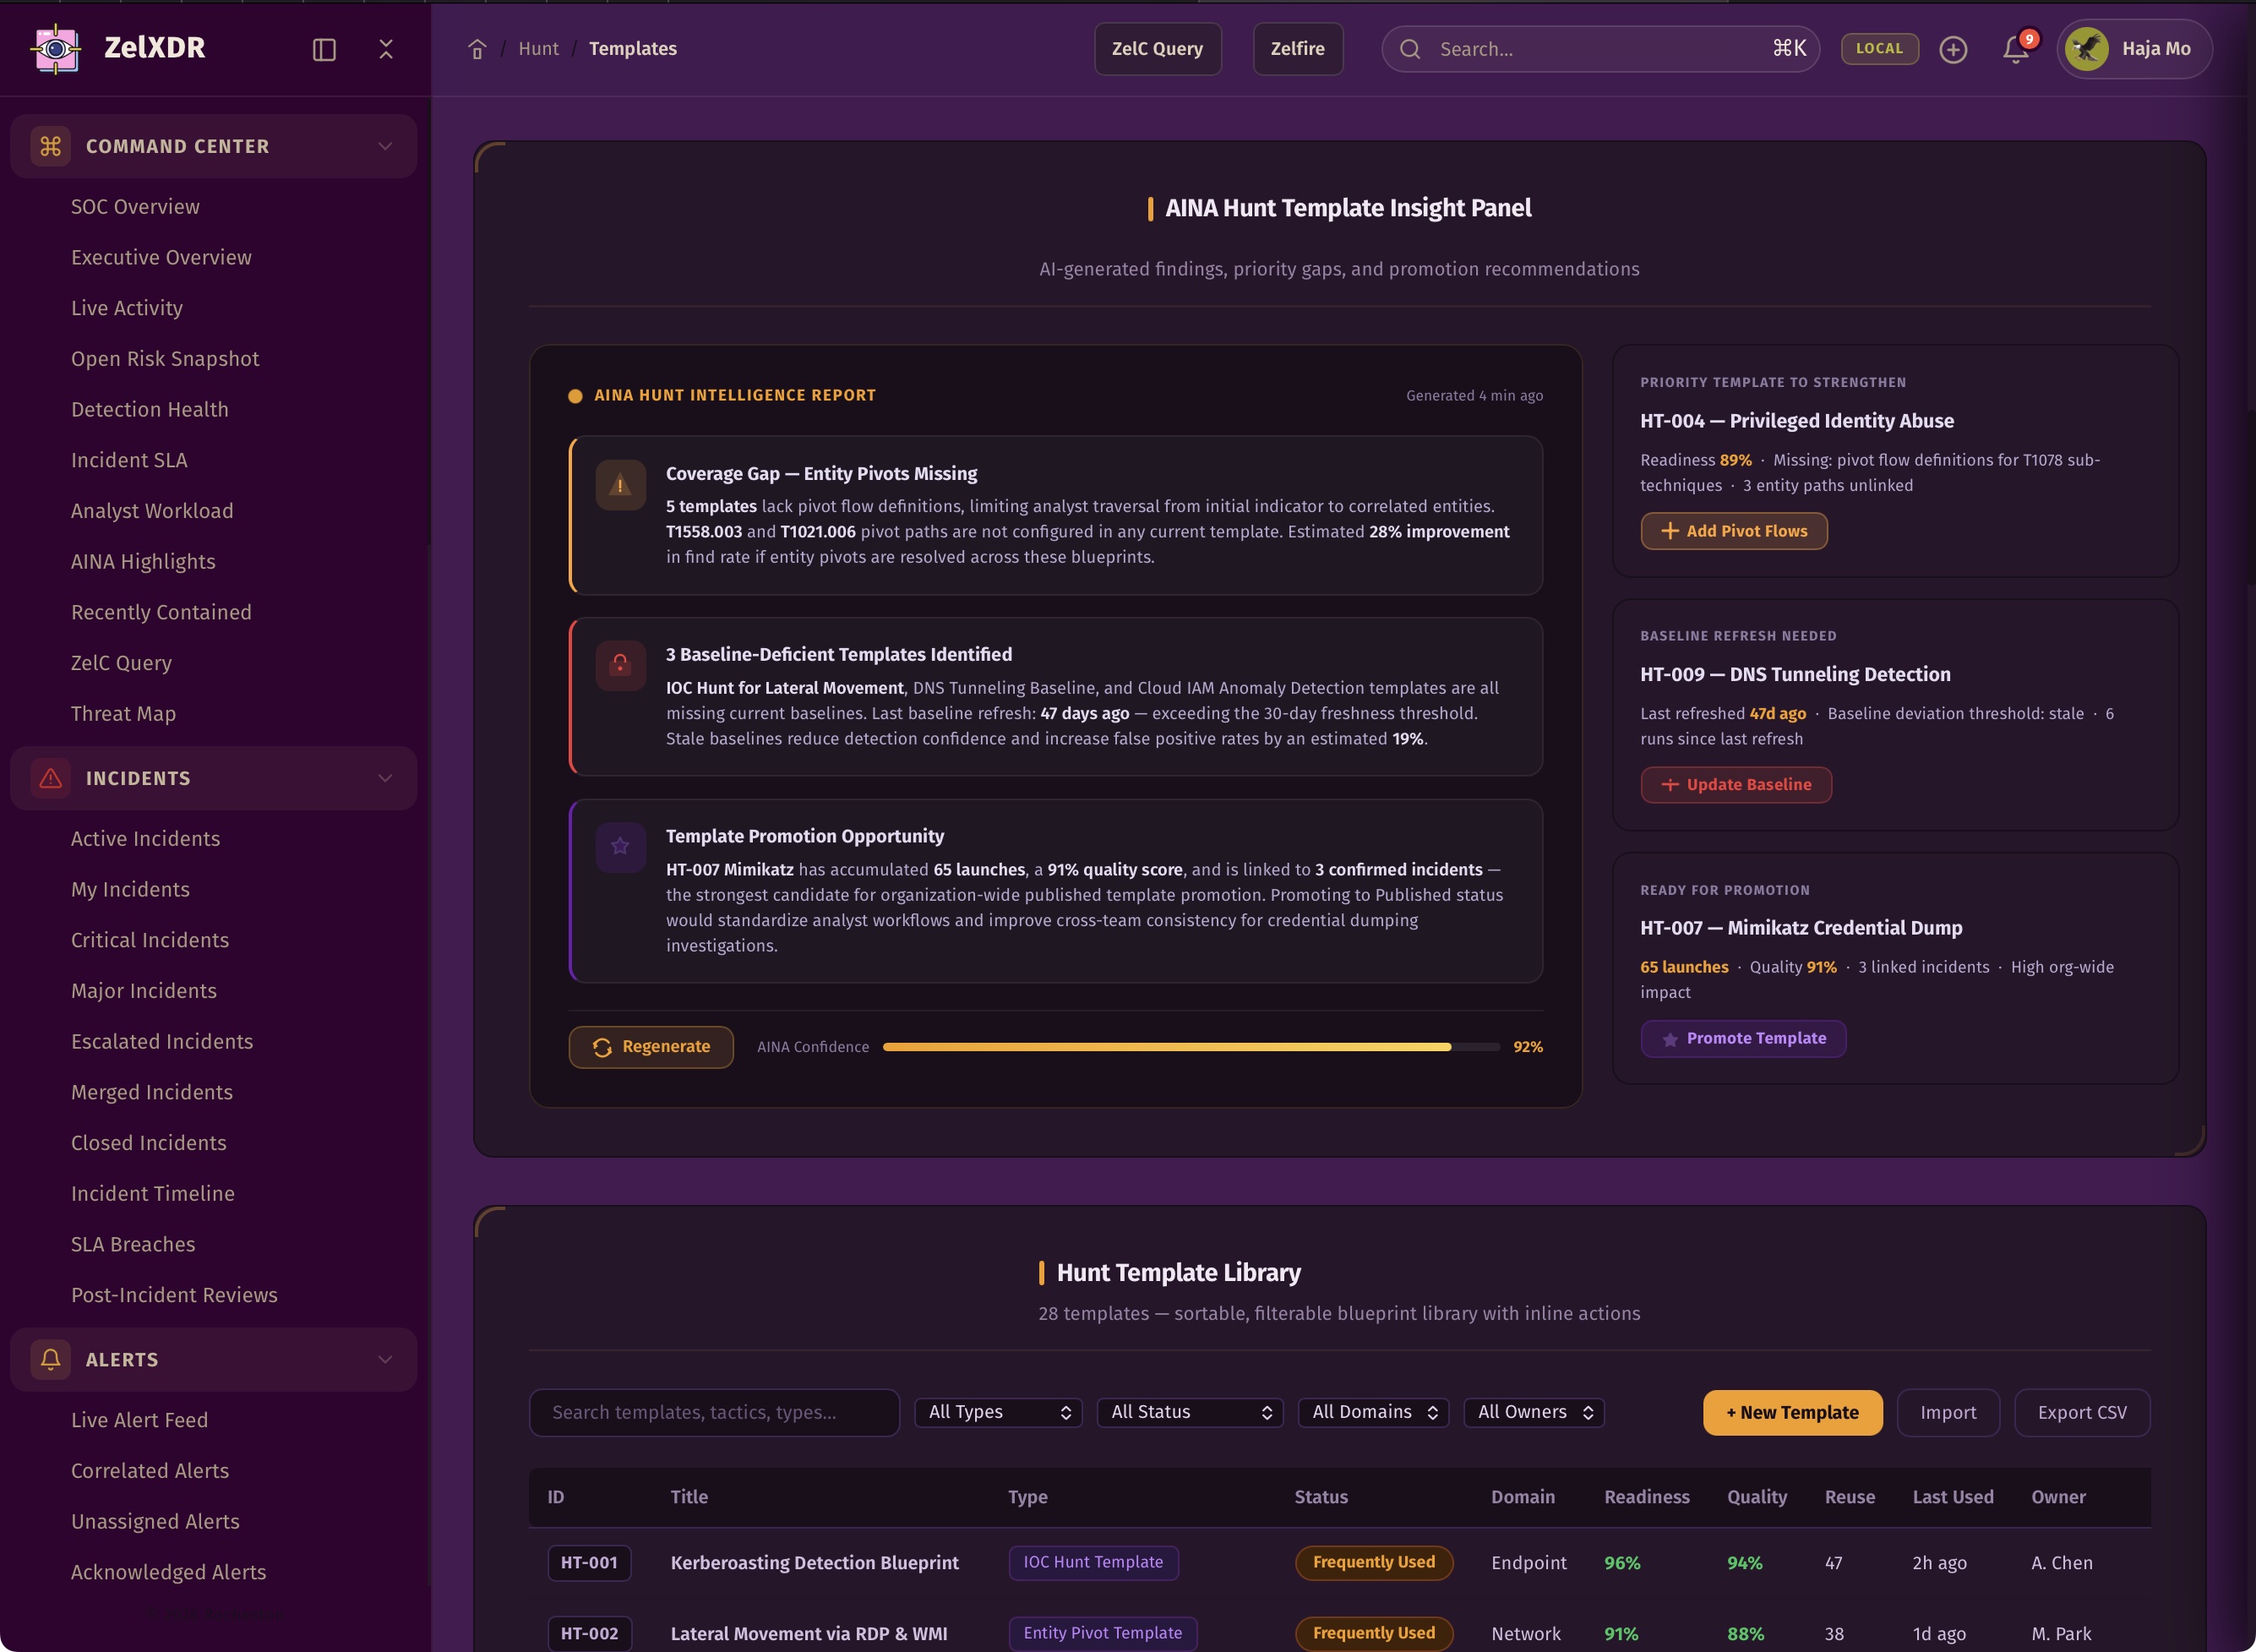
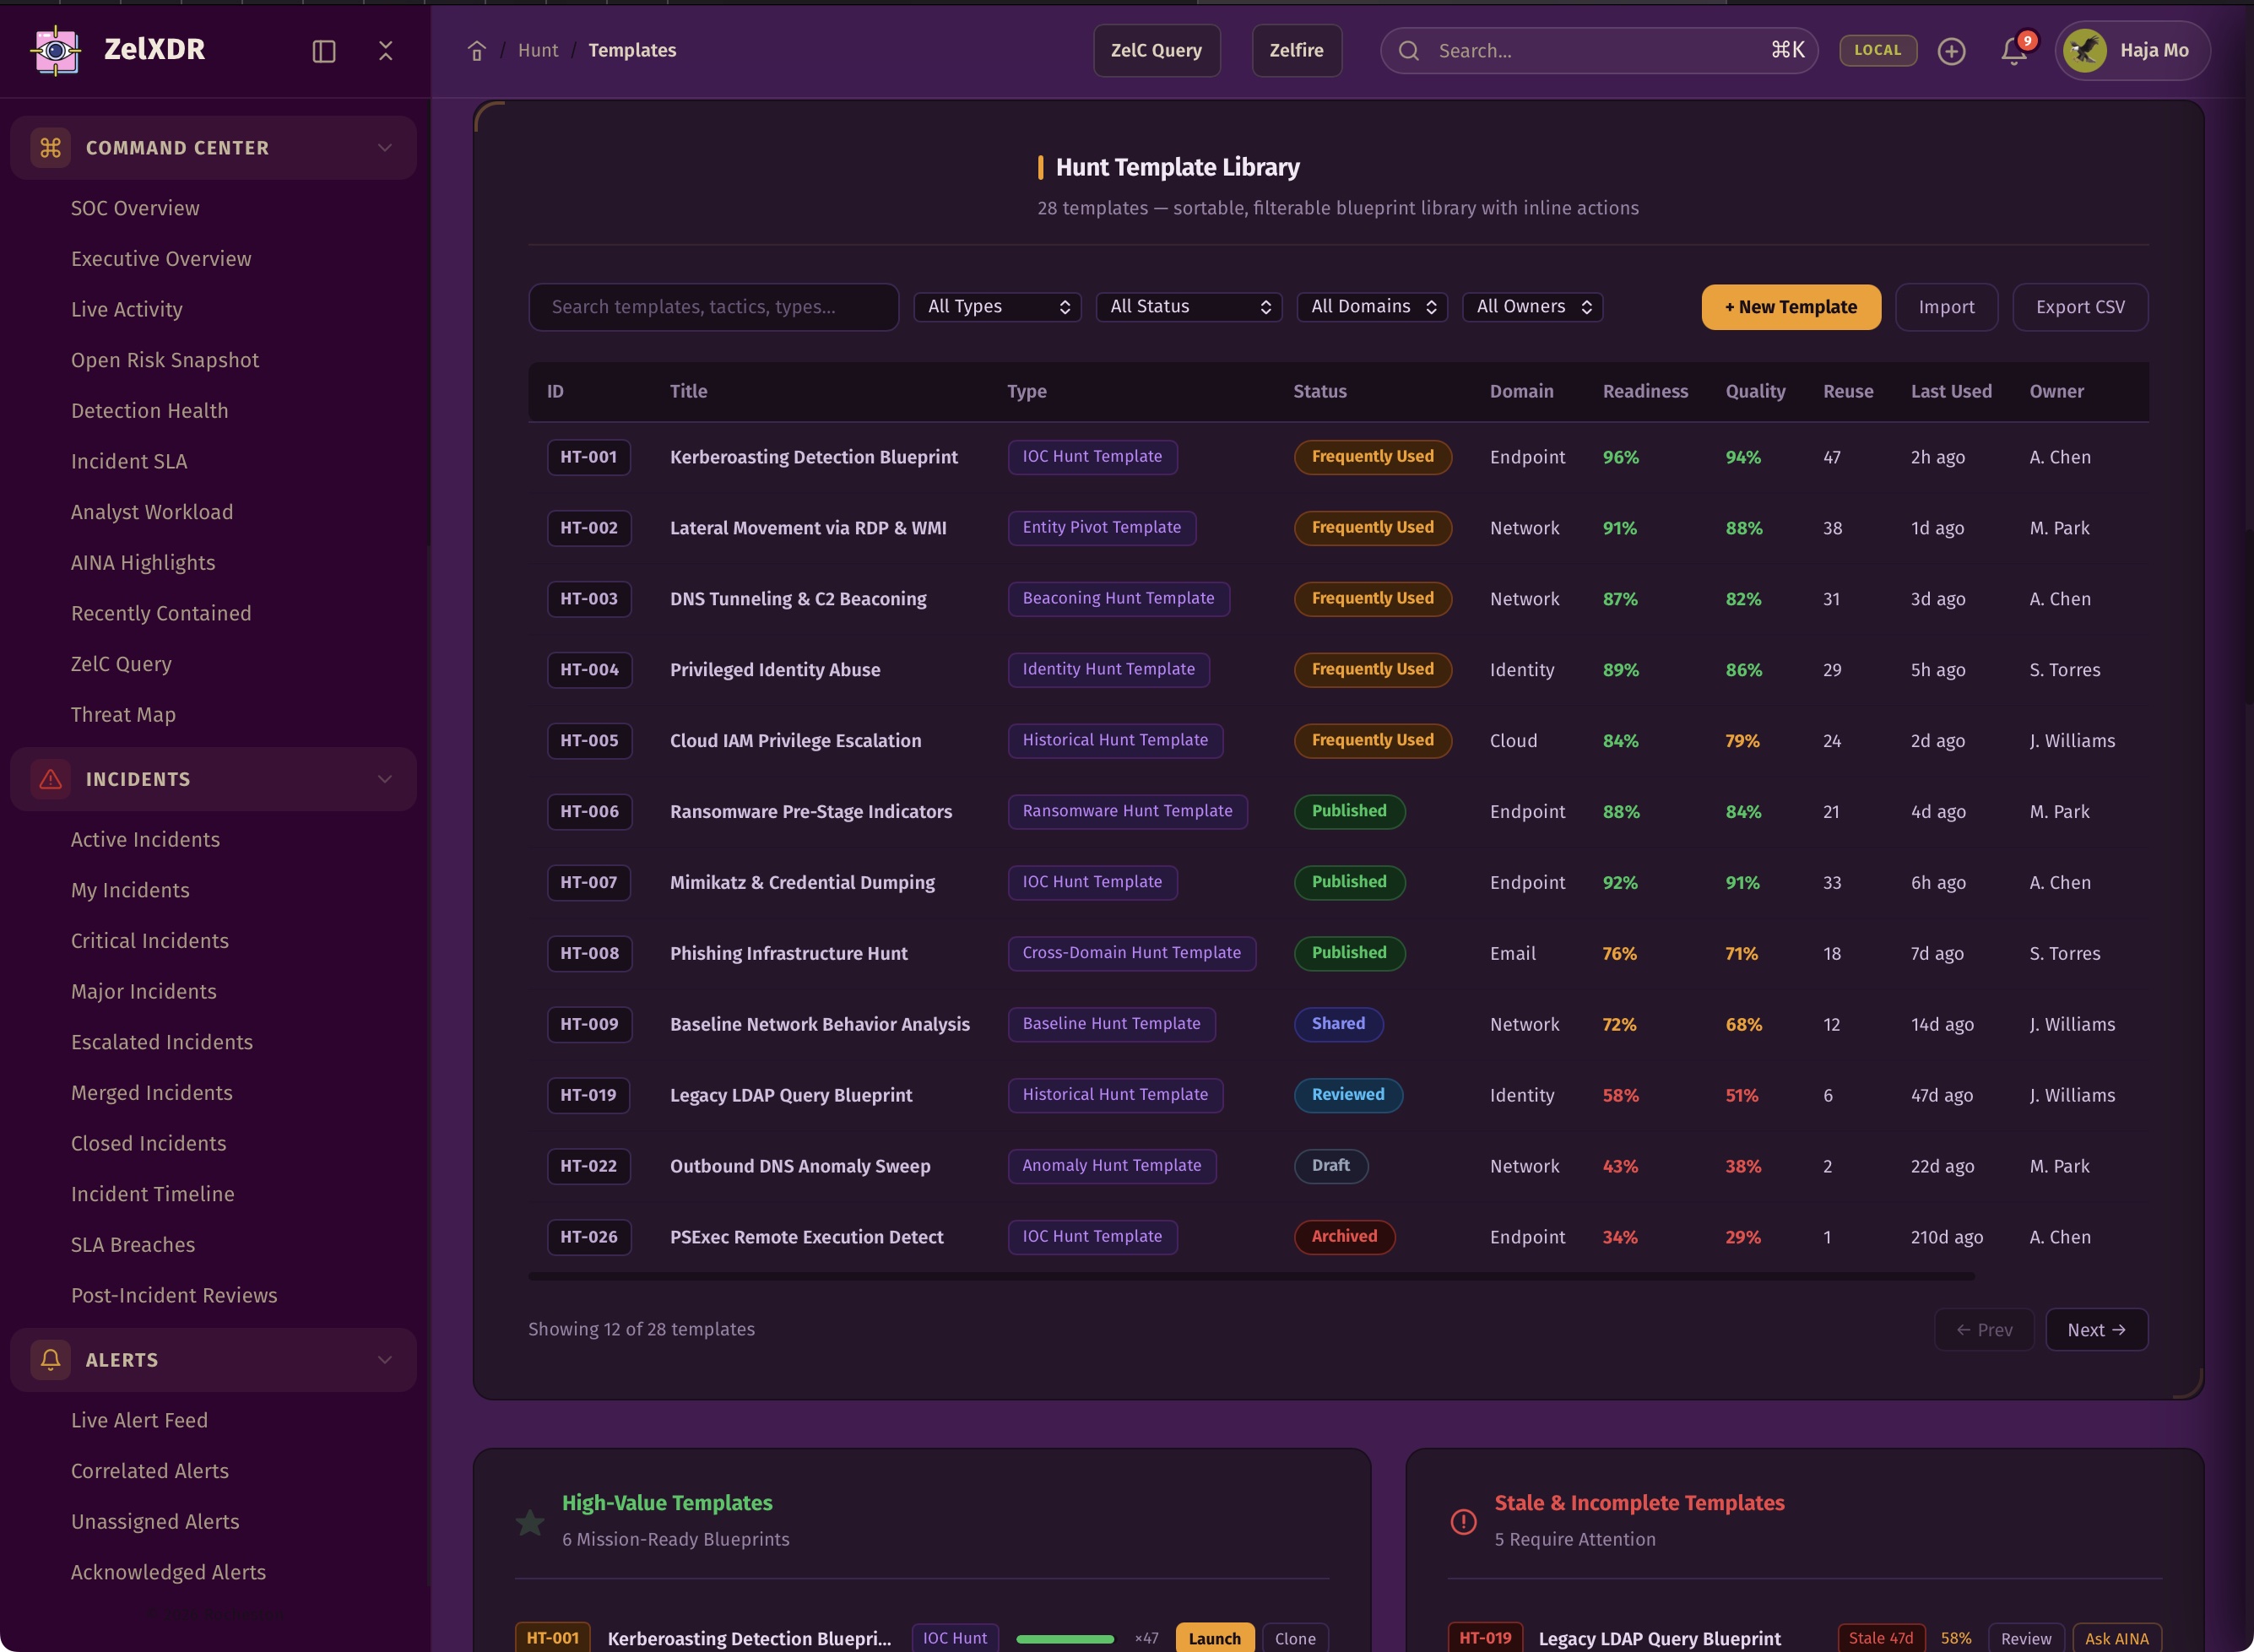
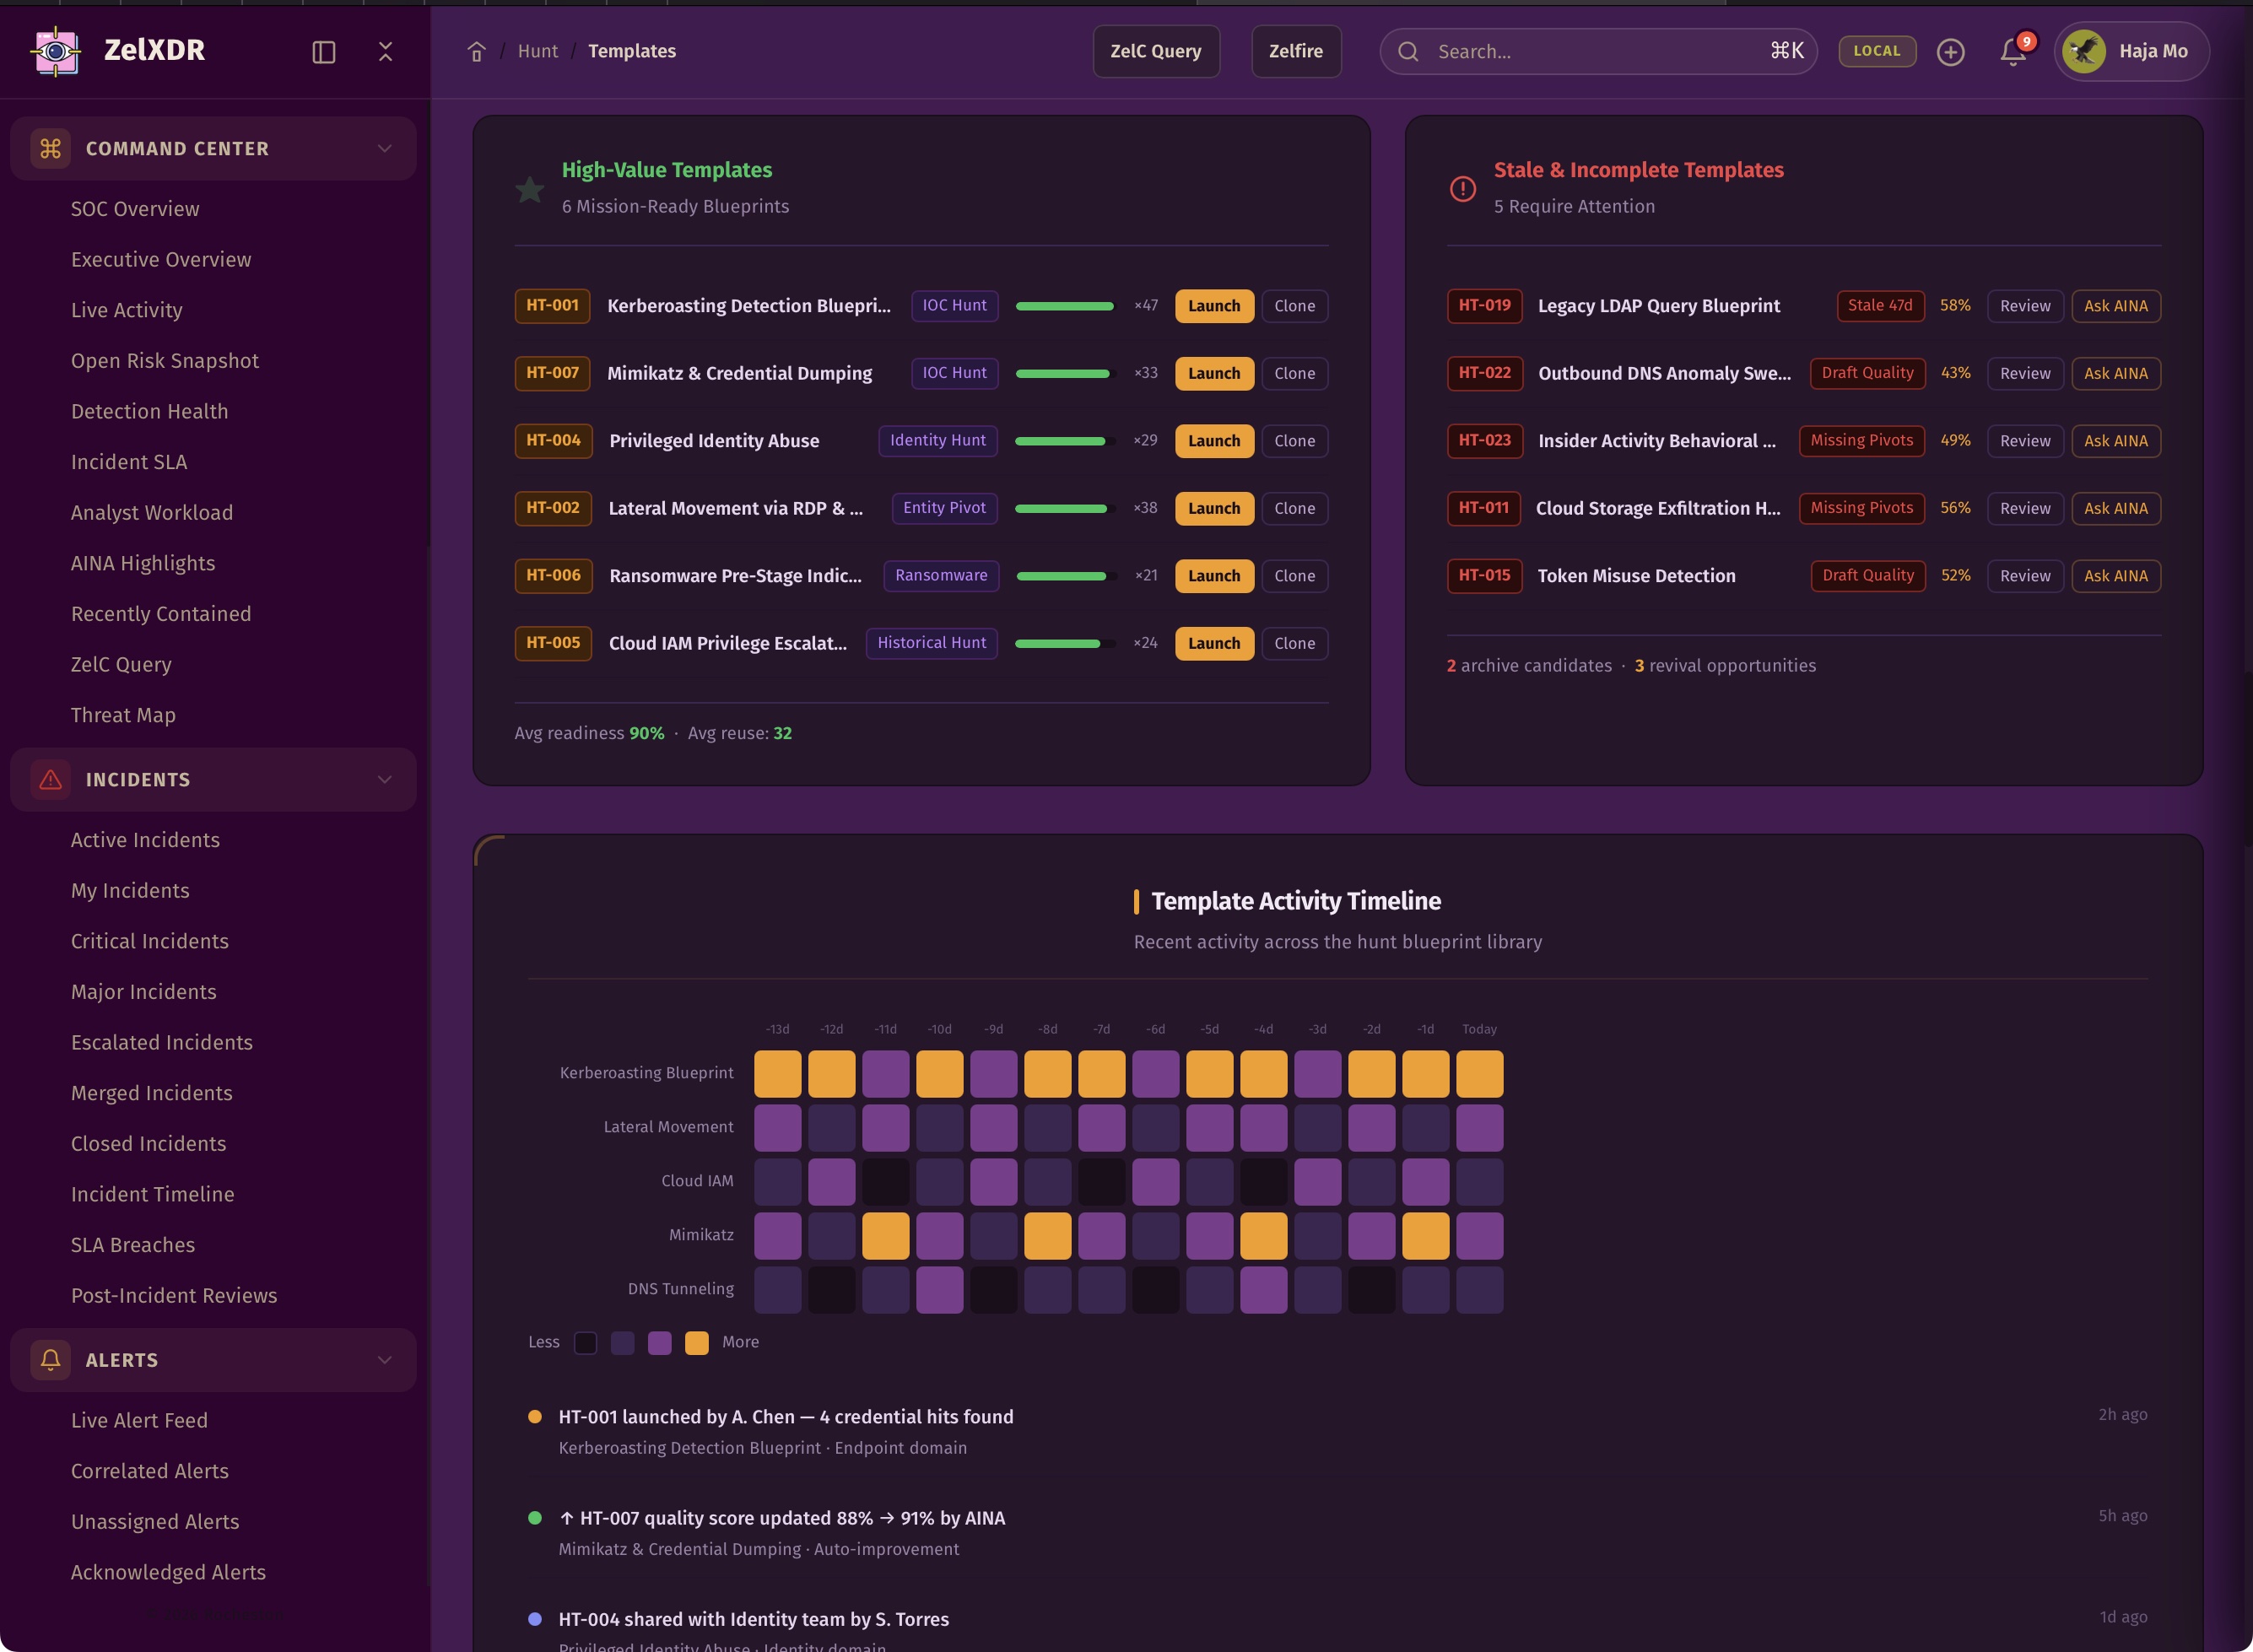
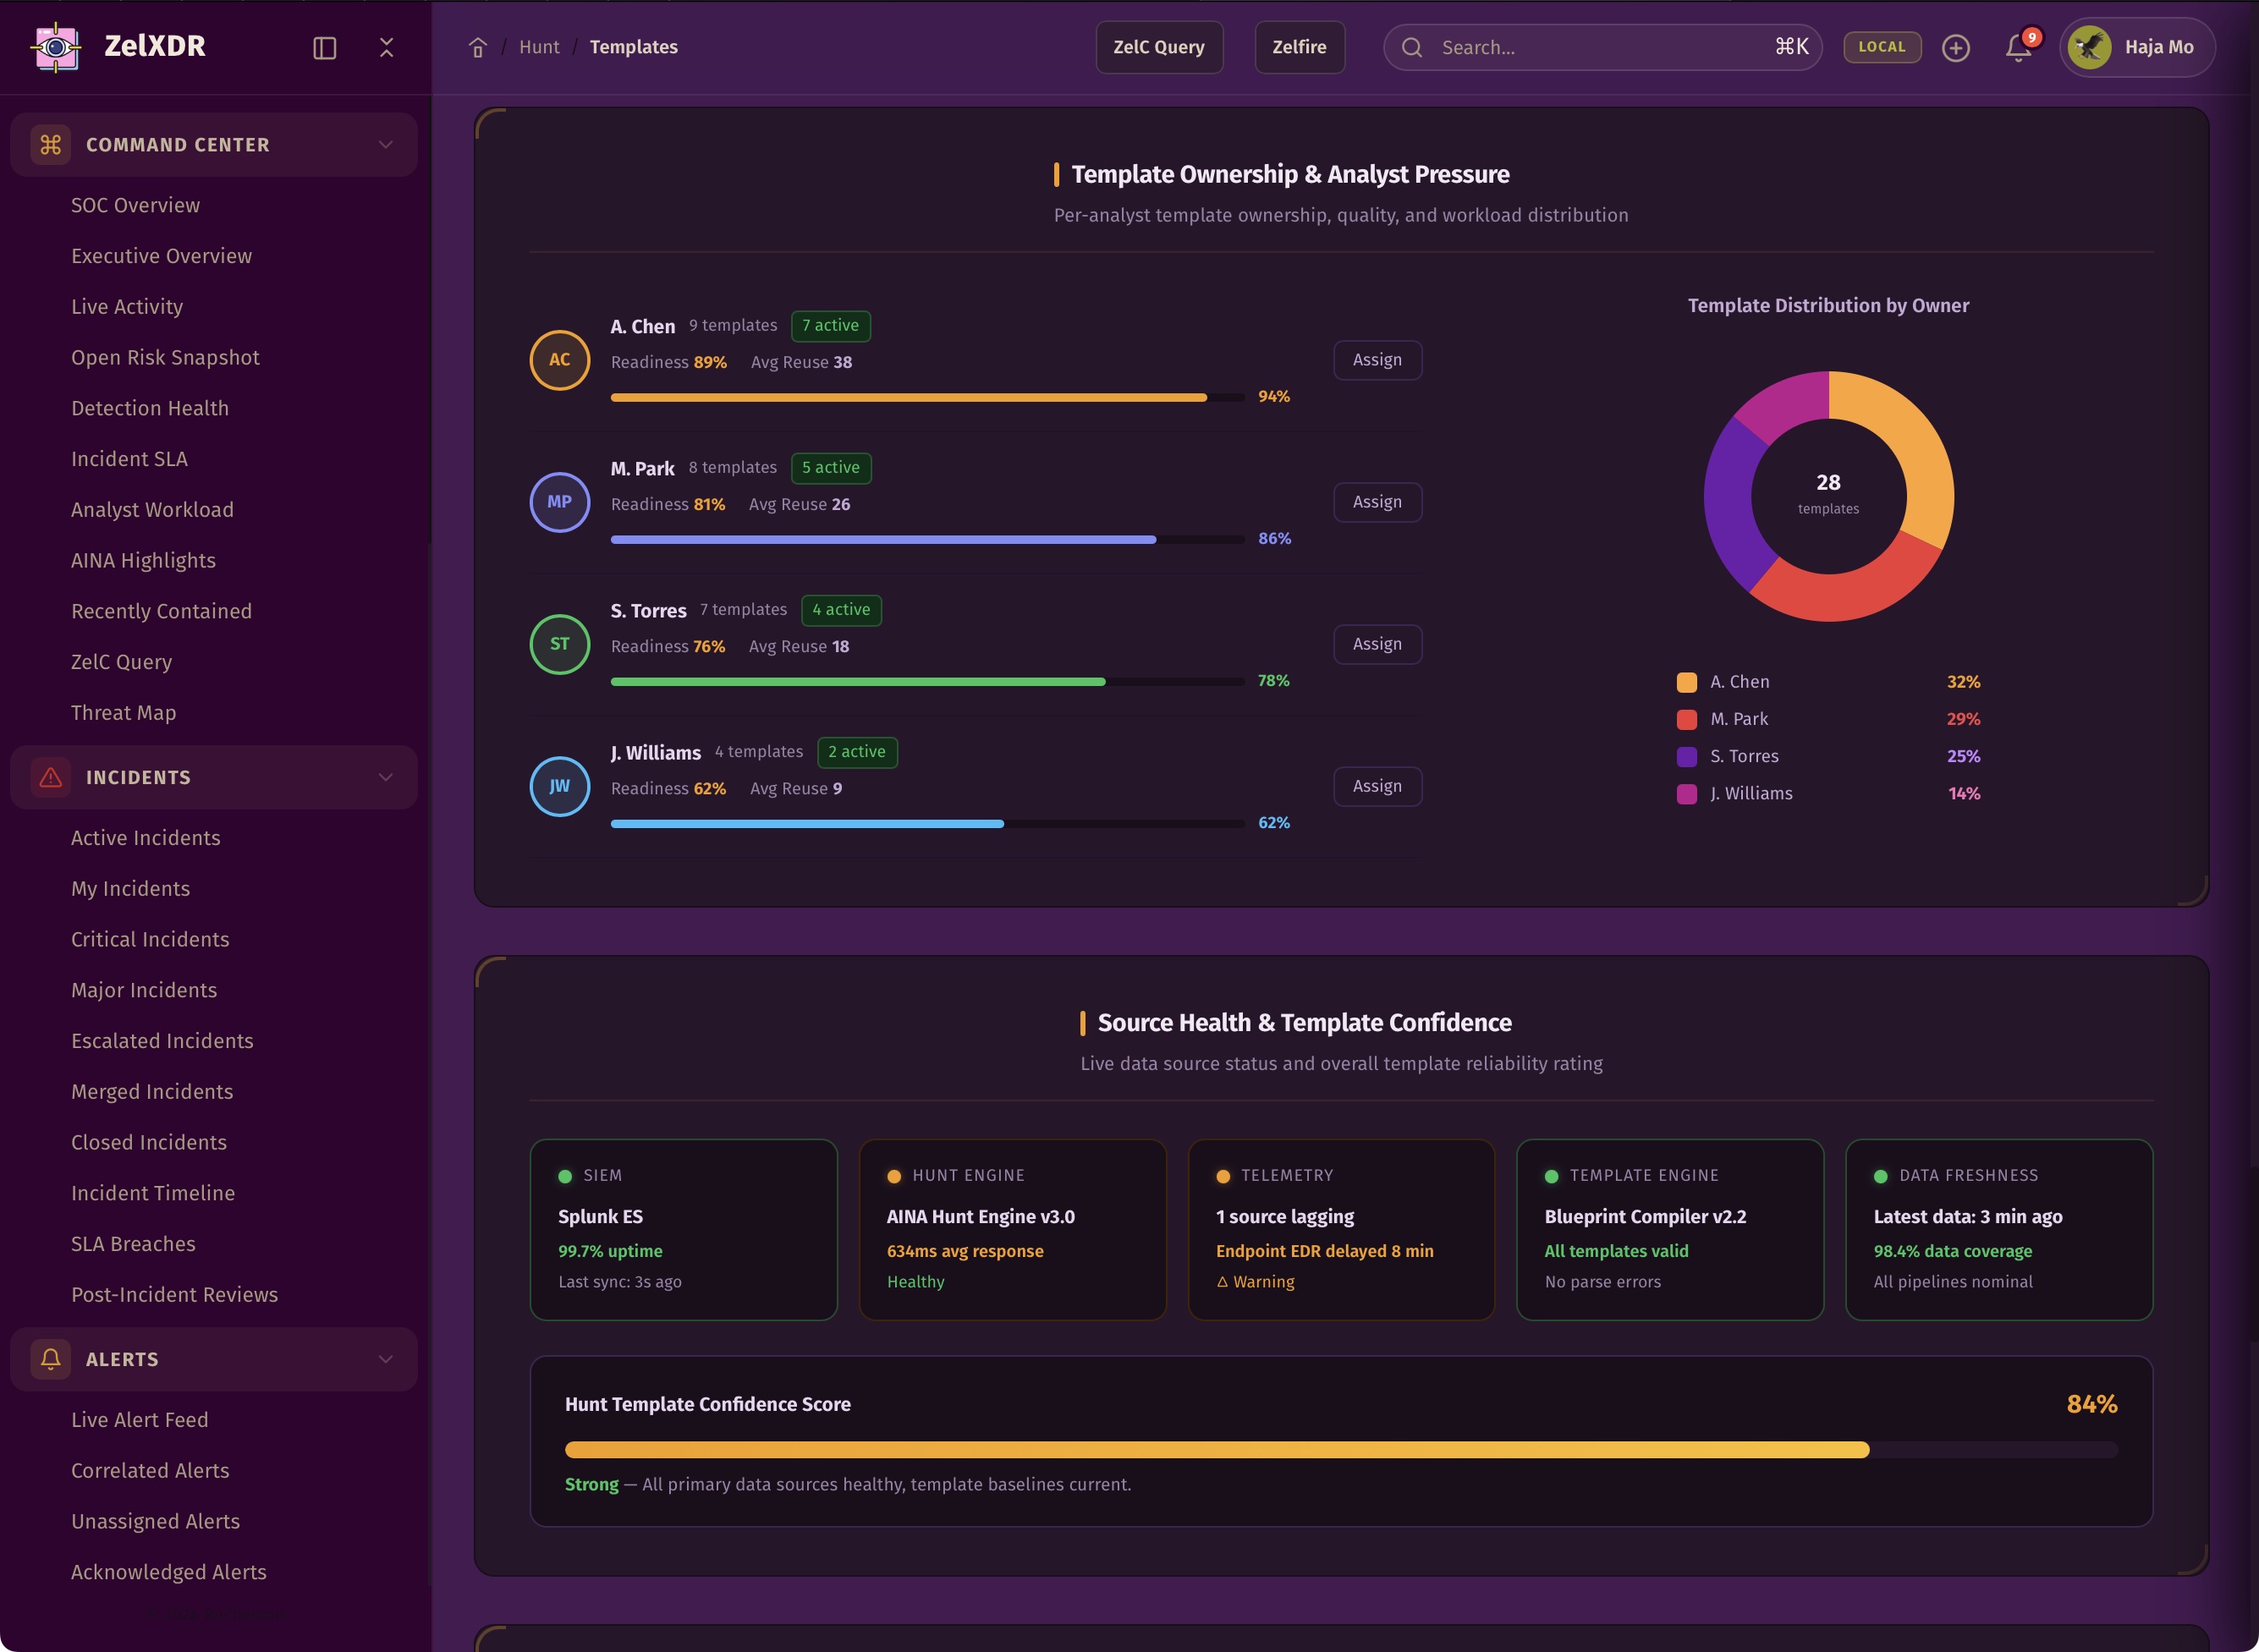
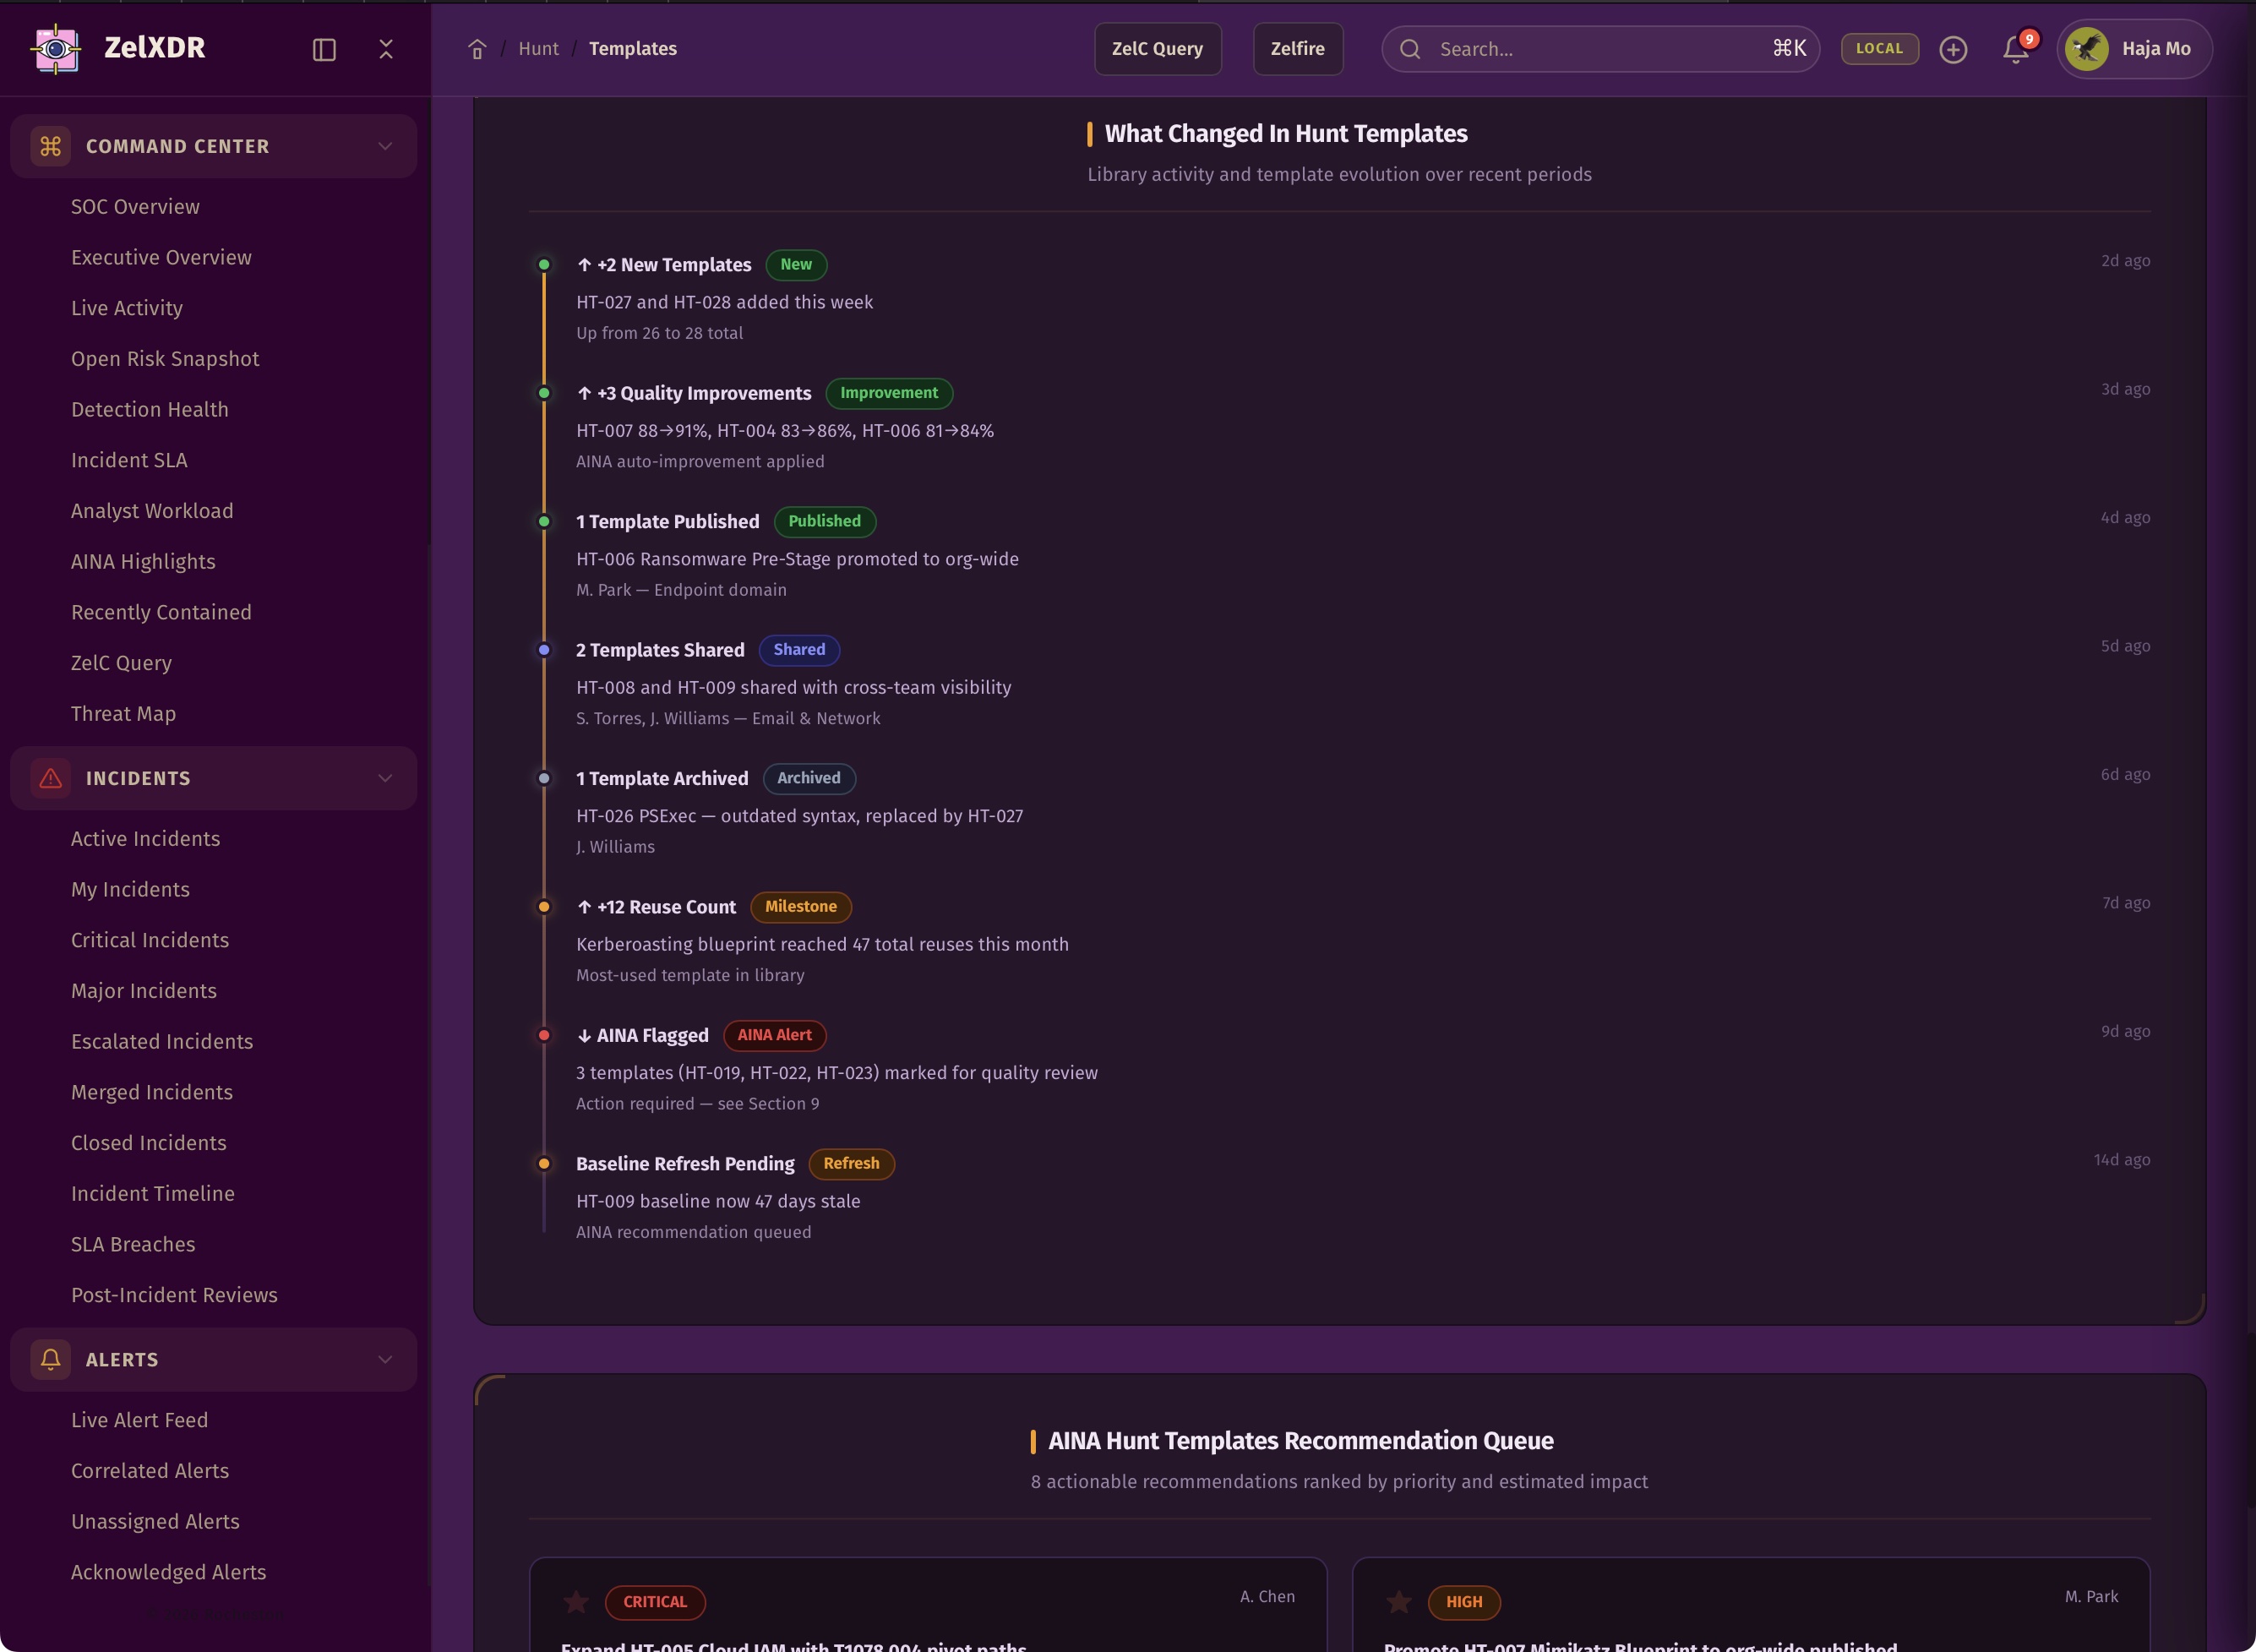
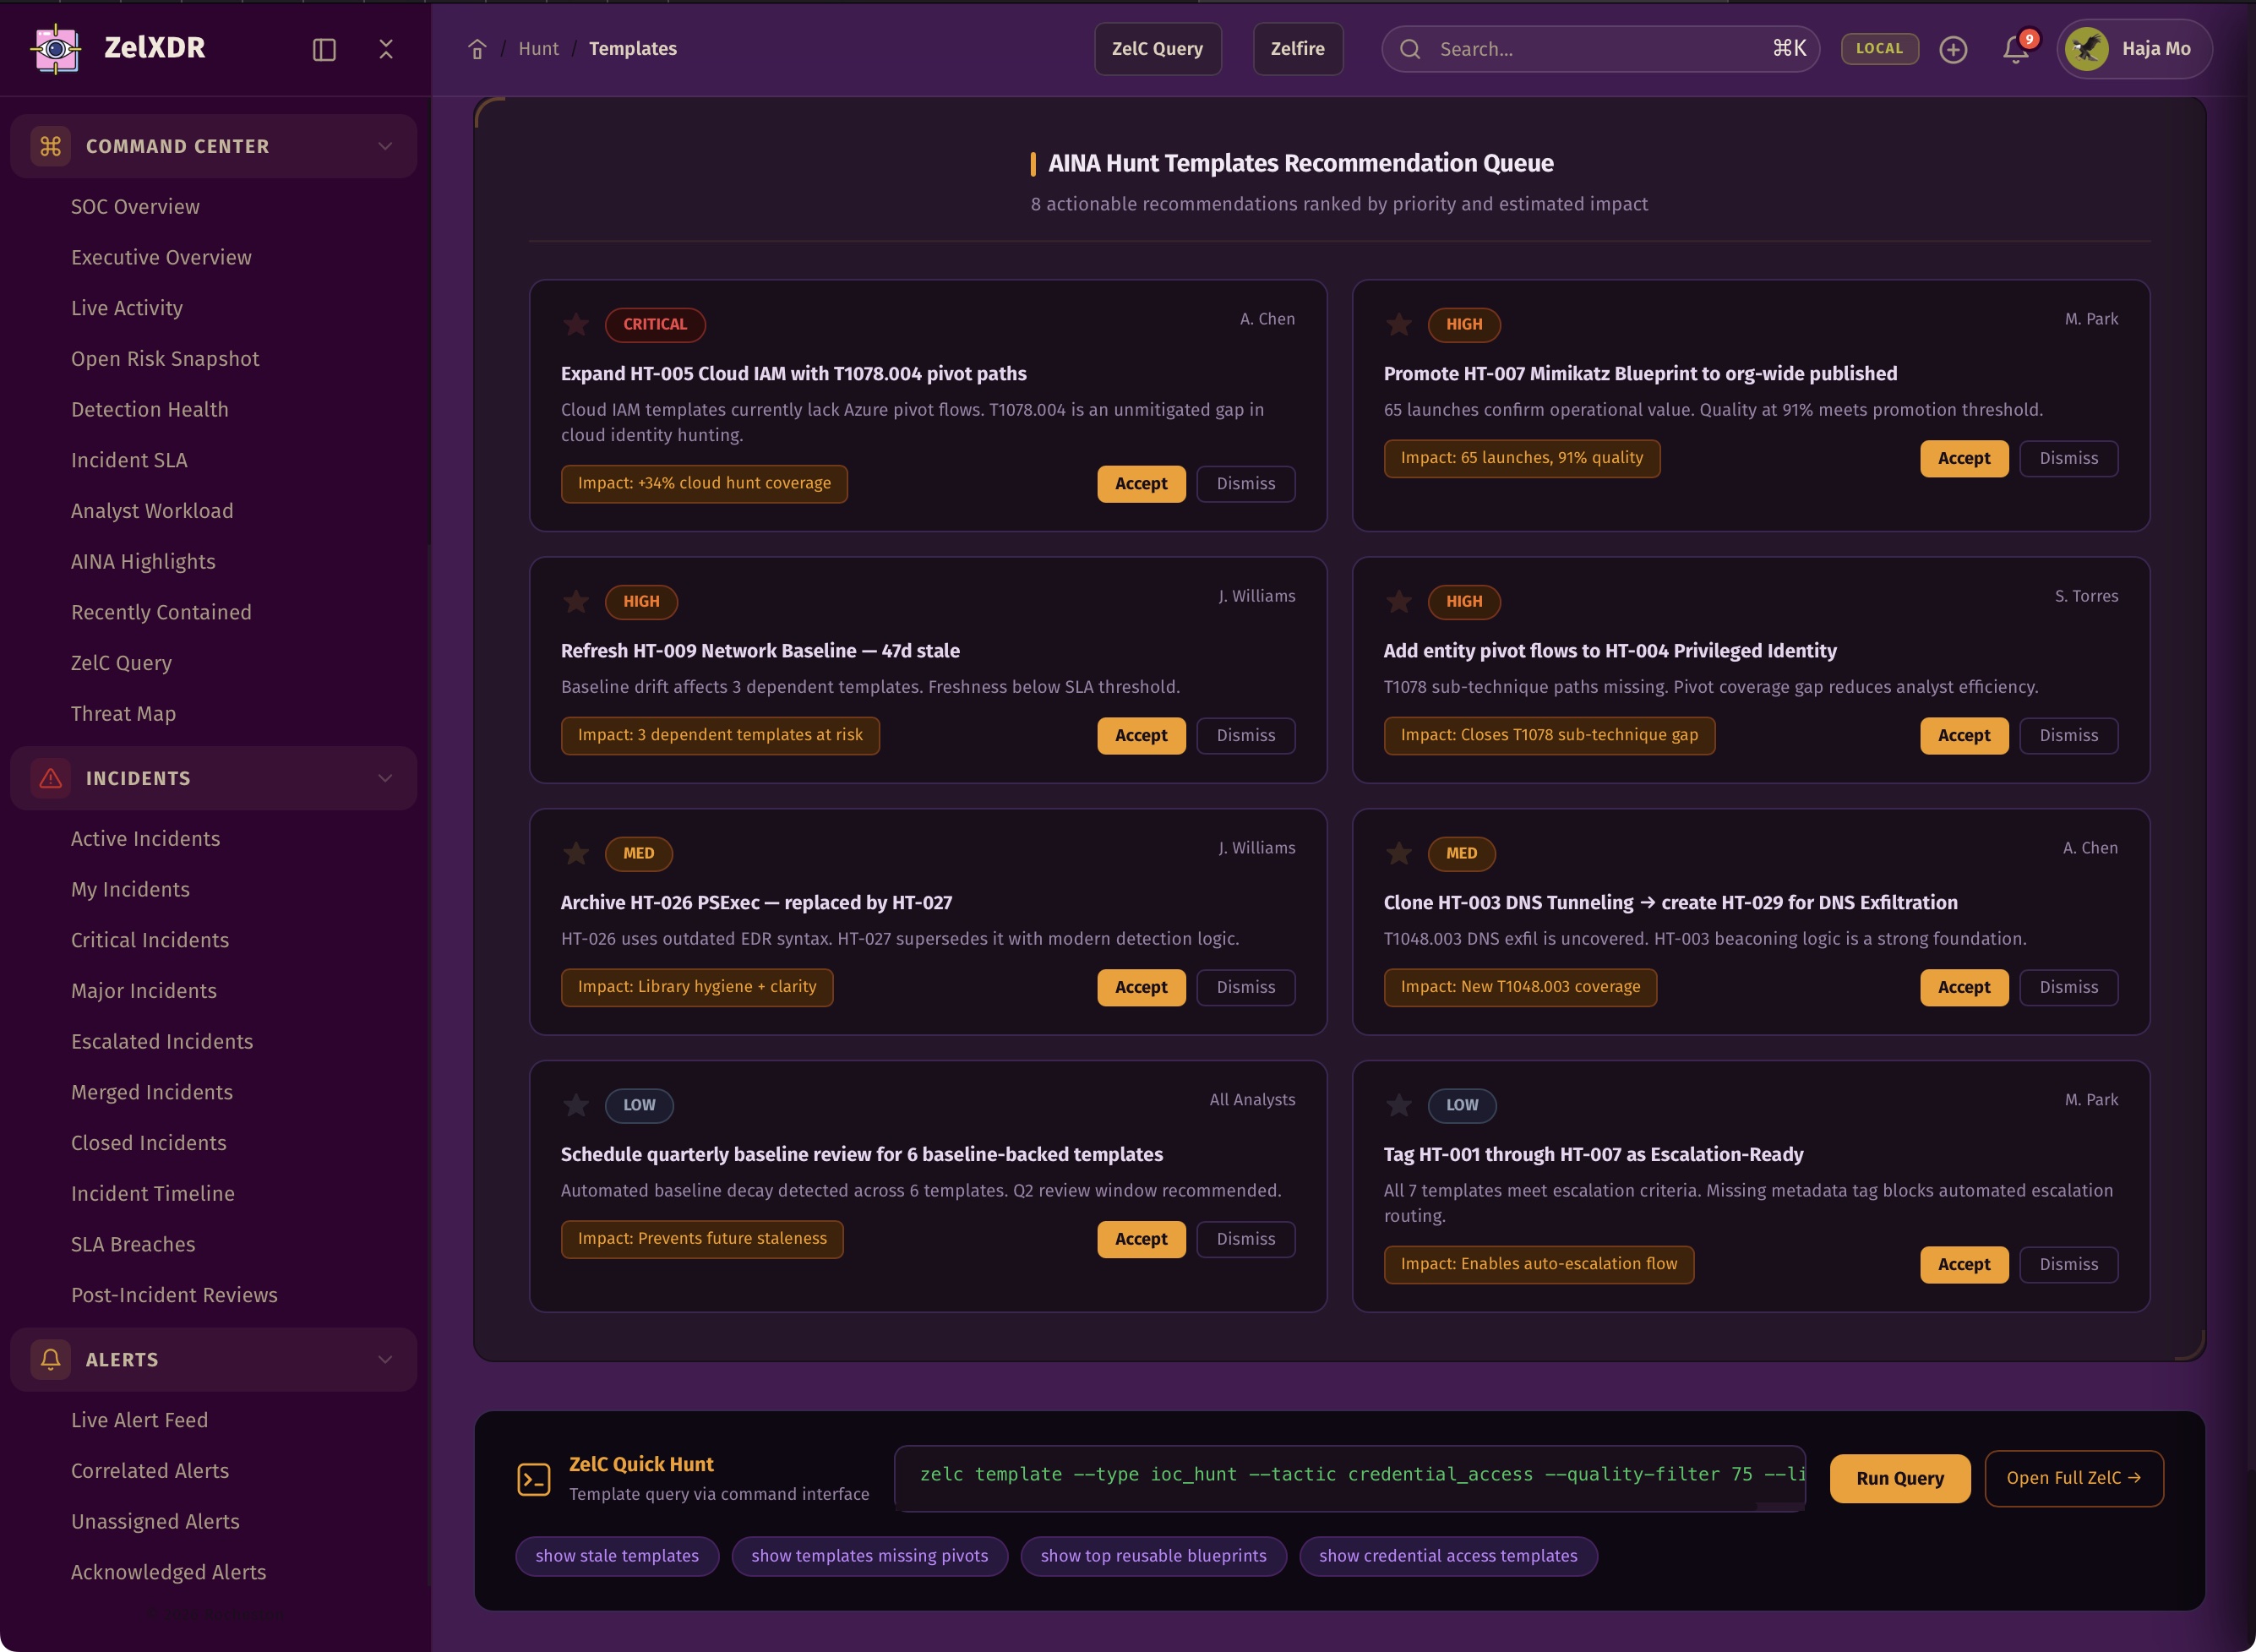
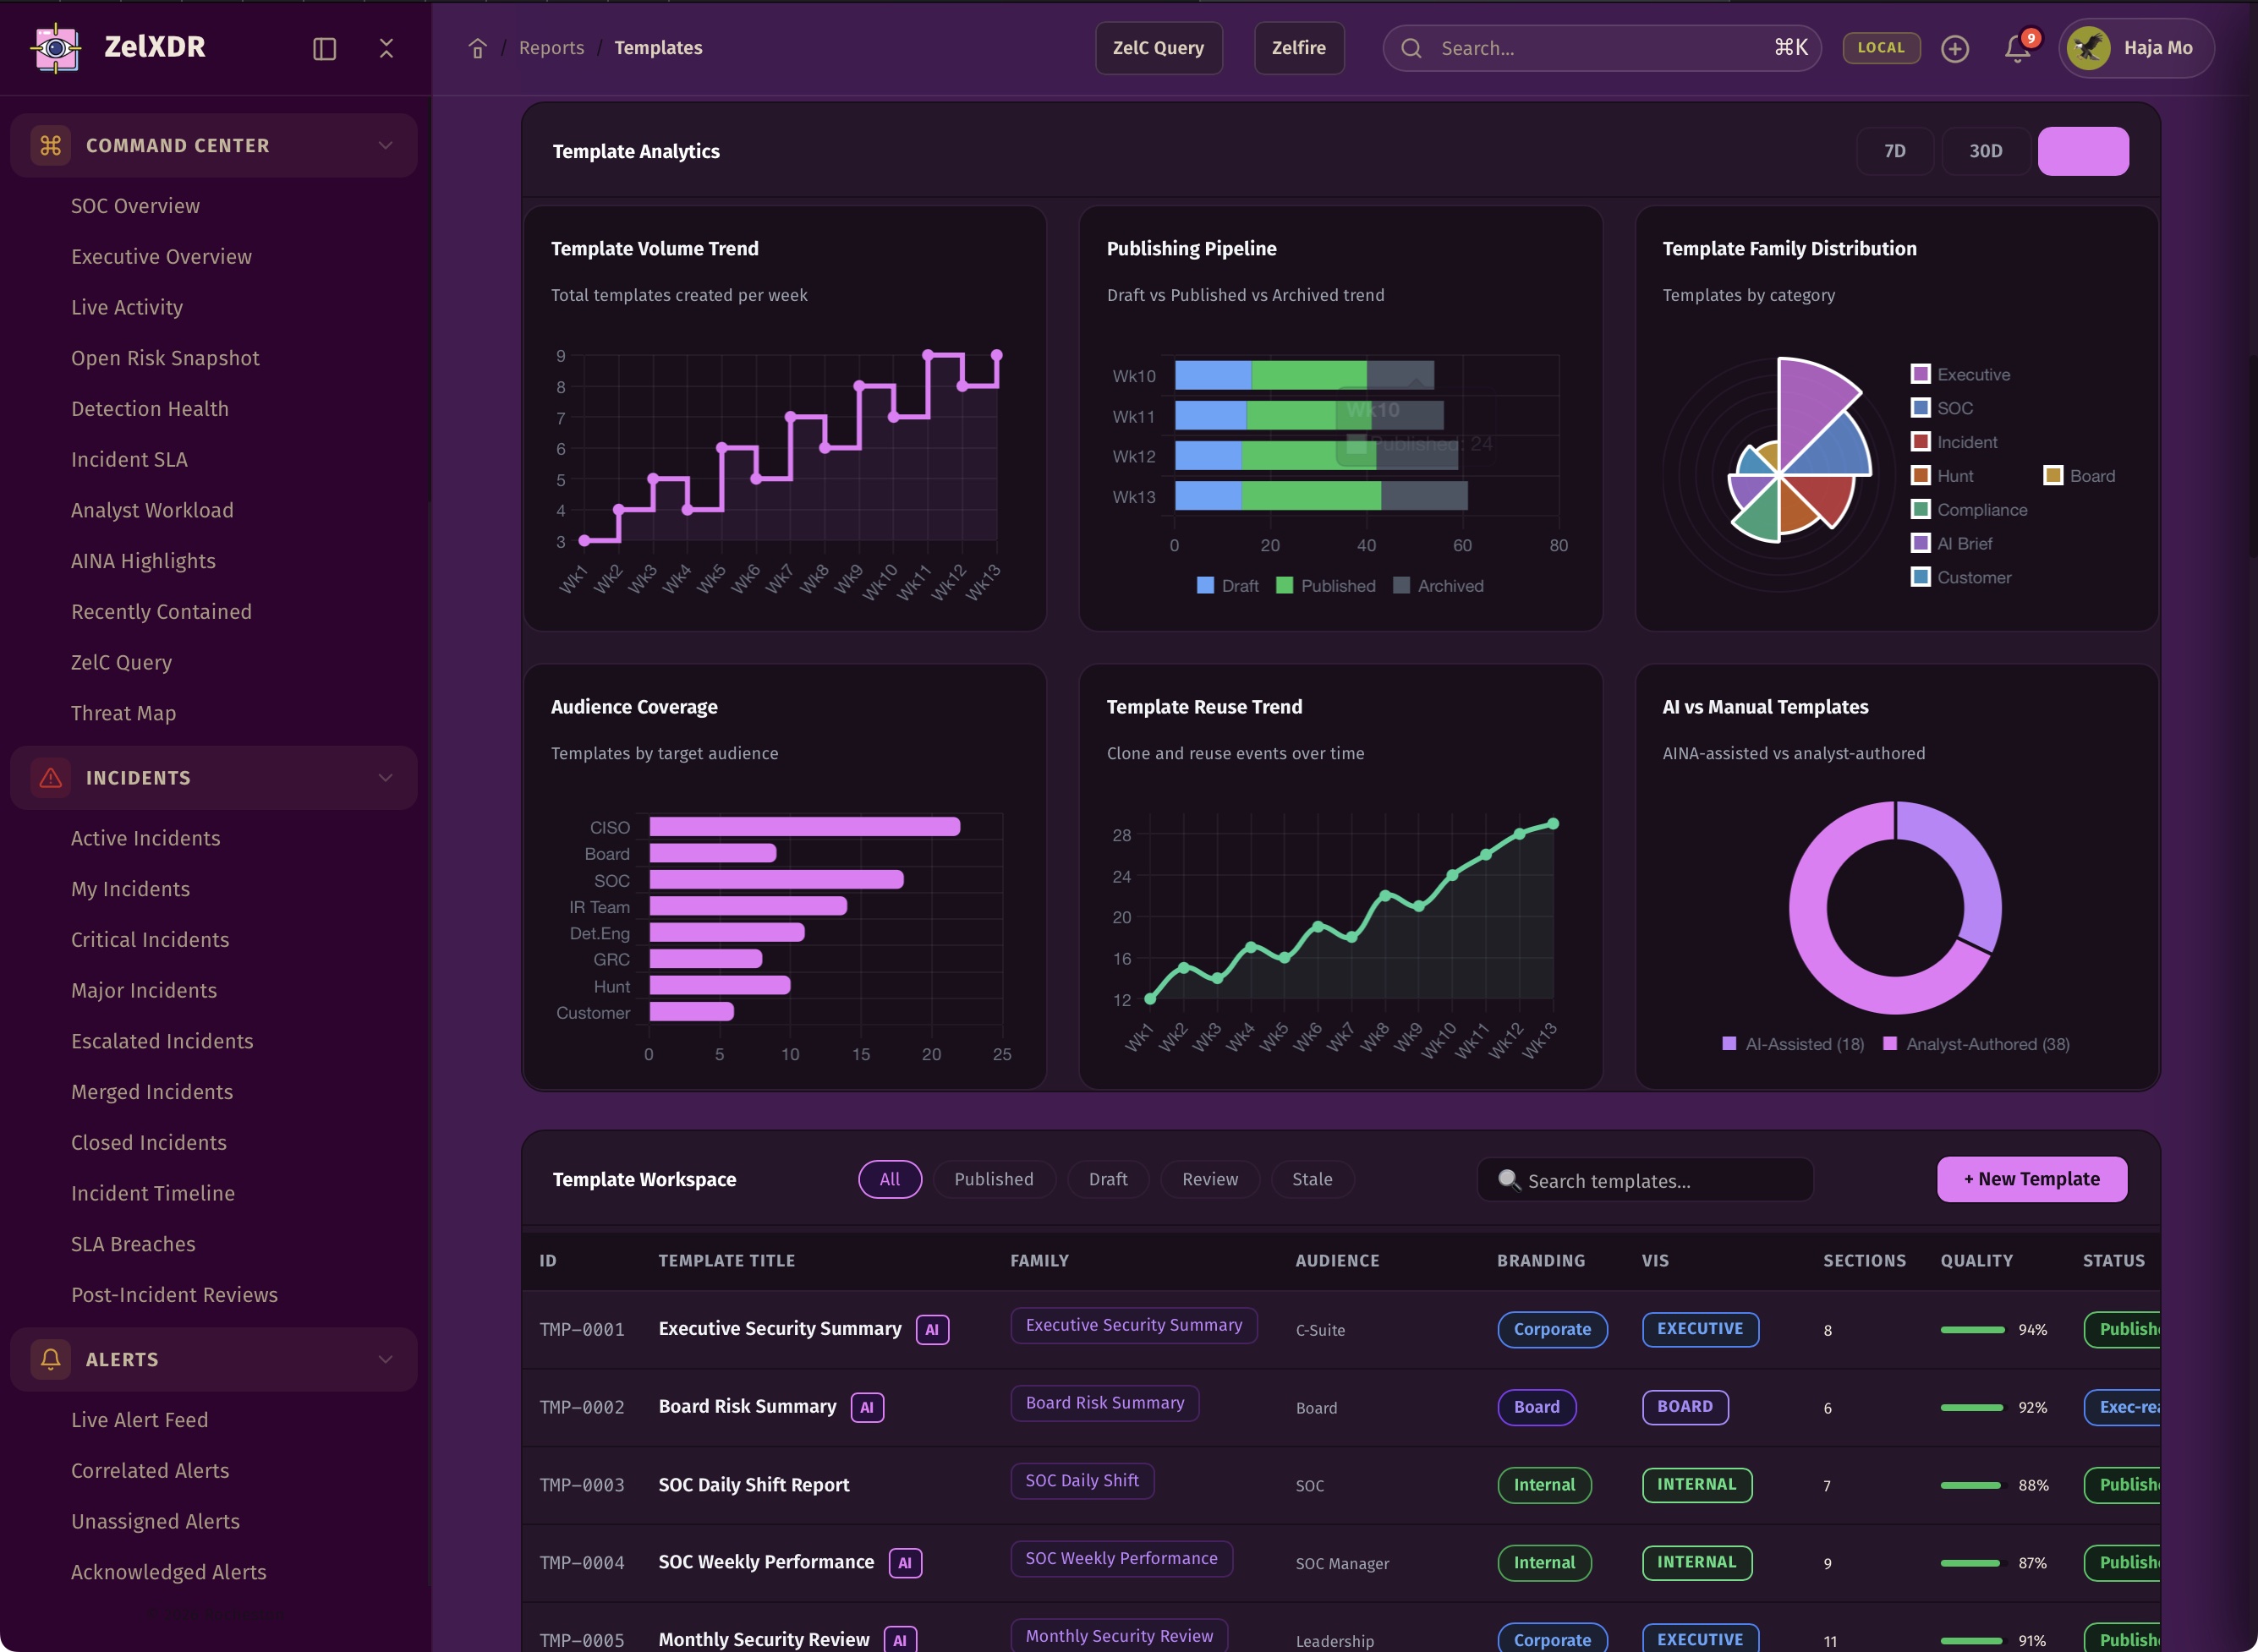
Hunt Templates let teams standardize recurring hunt patterns, query blocks, IOC paths, pivot flows, and escalation outcomes. This makes threat hunting more repeatable and more scalable.
Templates turn experience into acceleration.
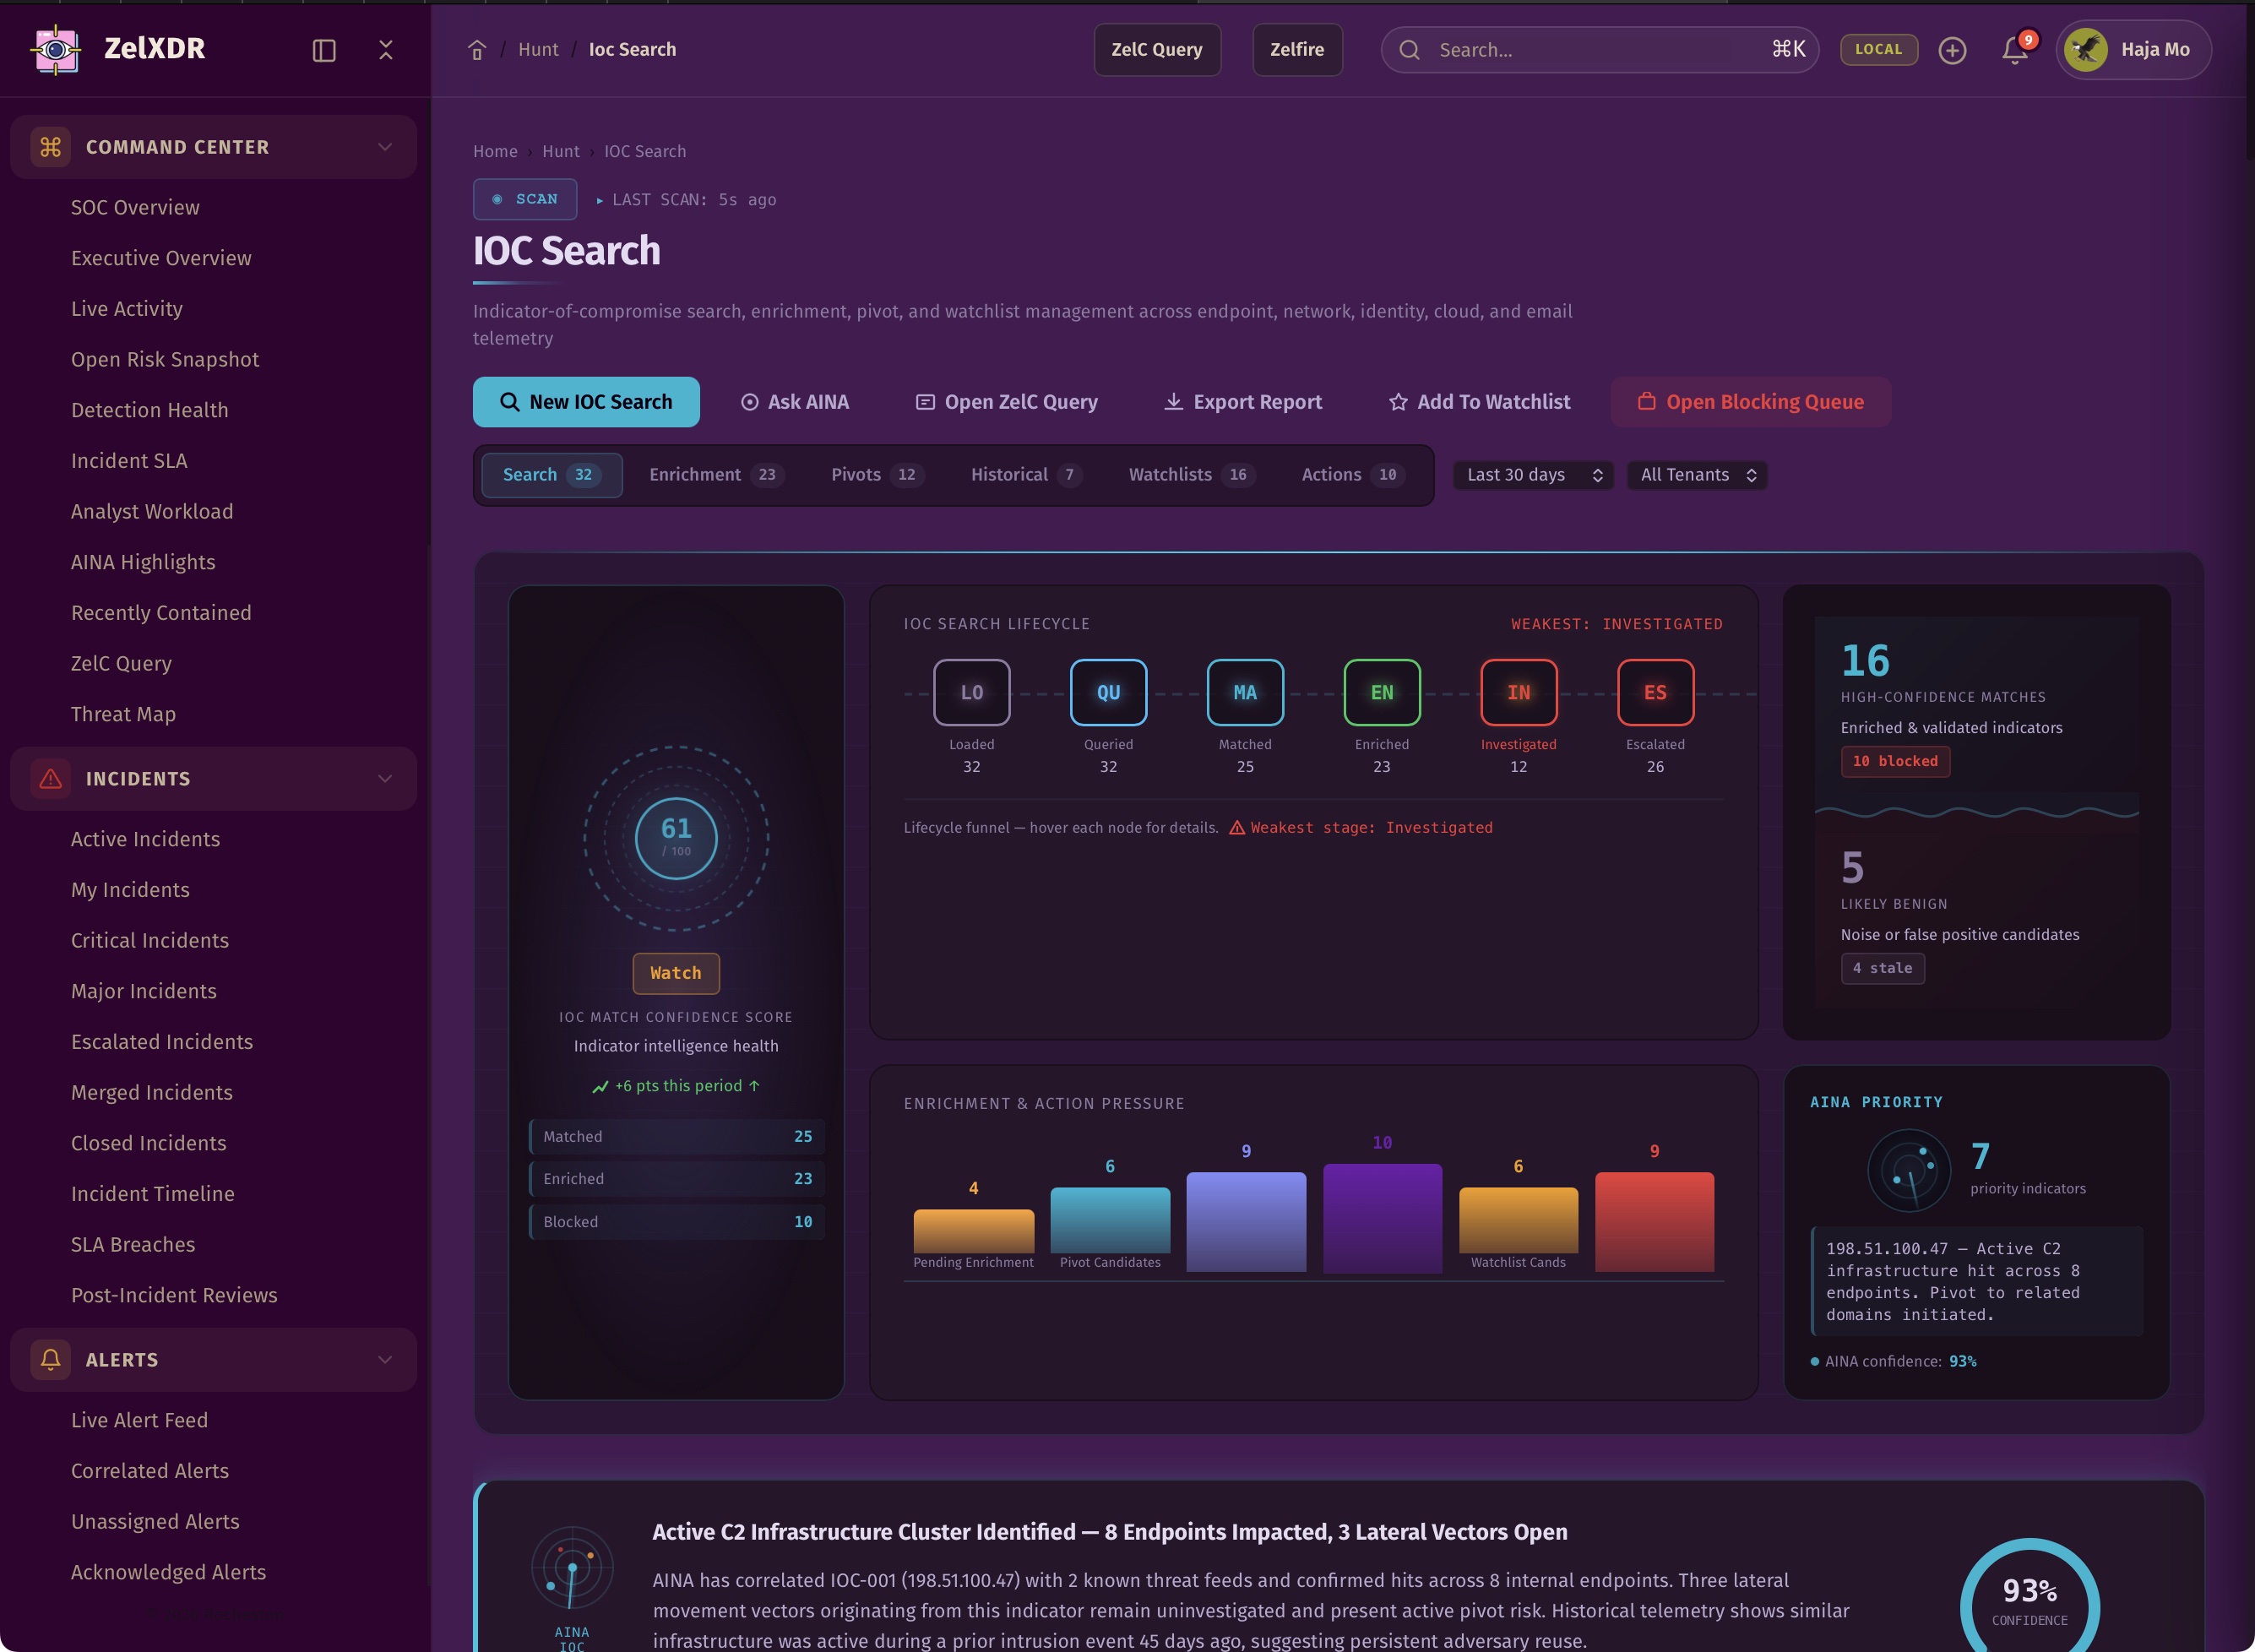
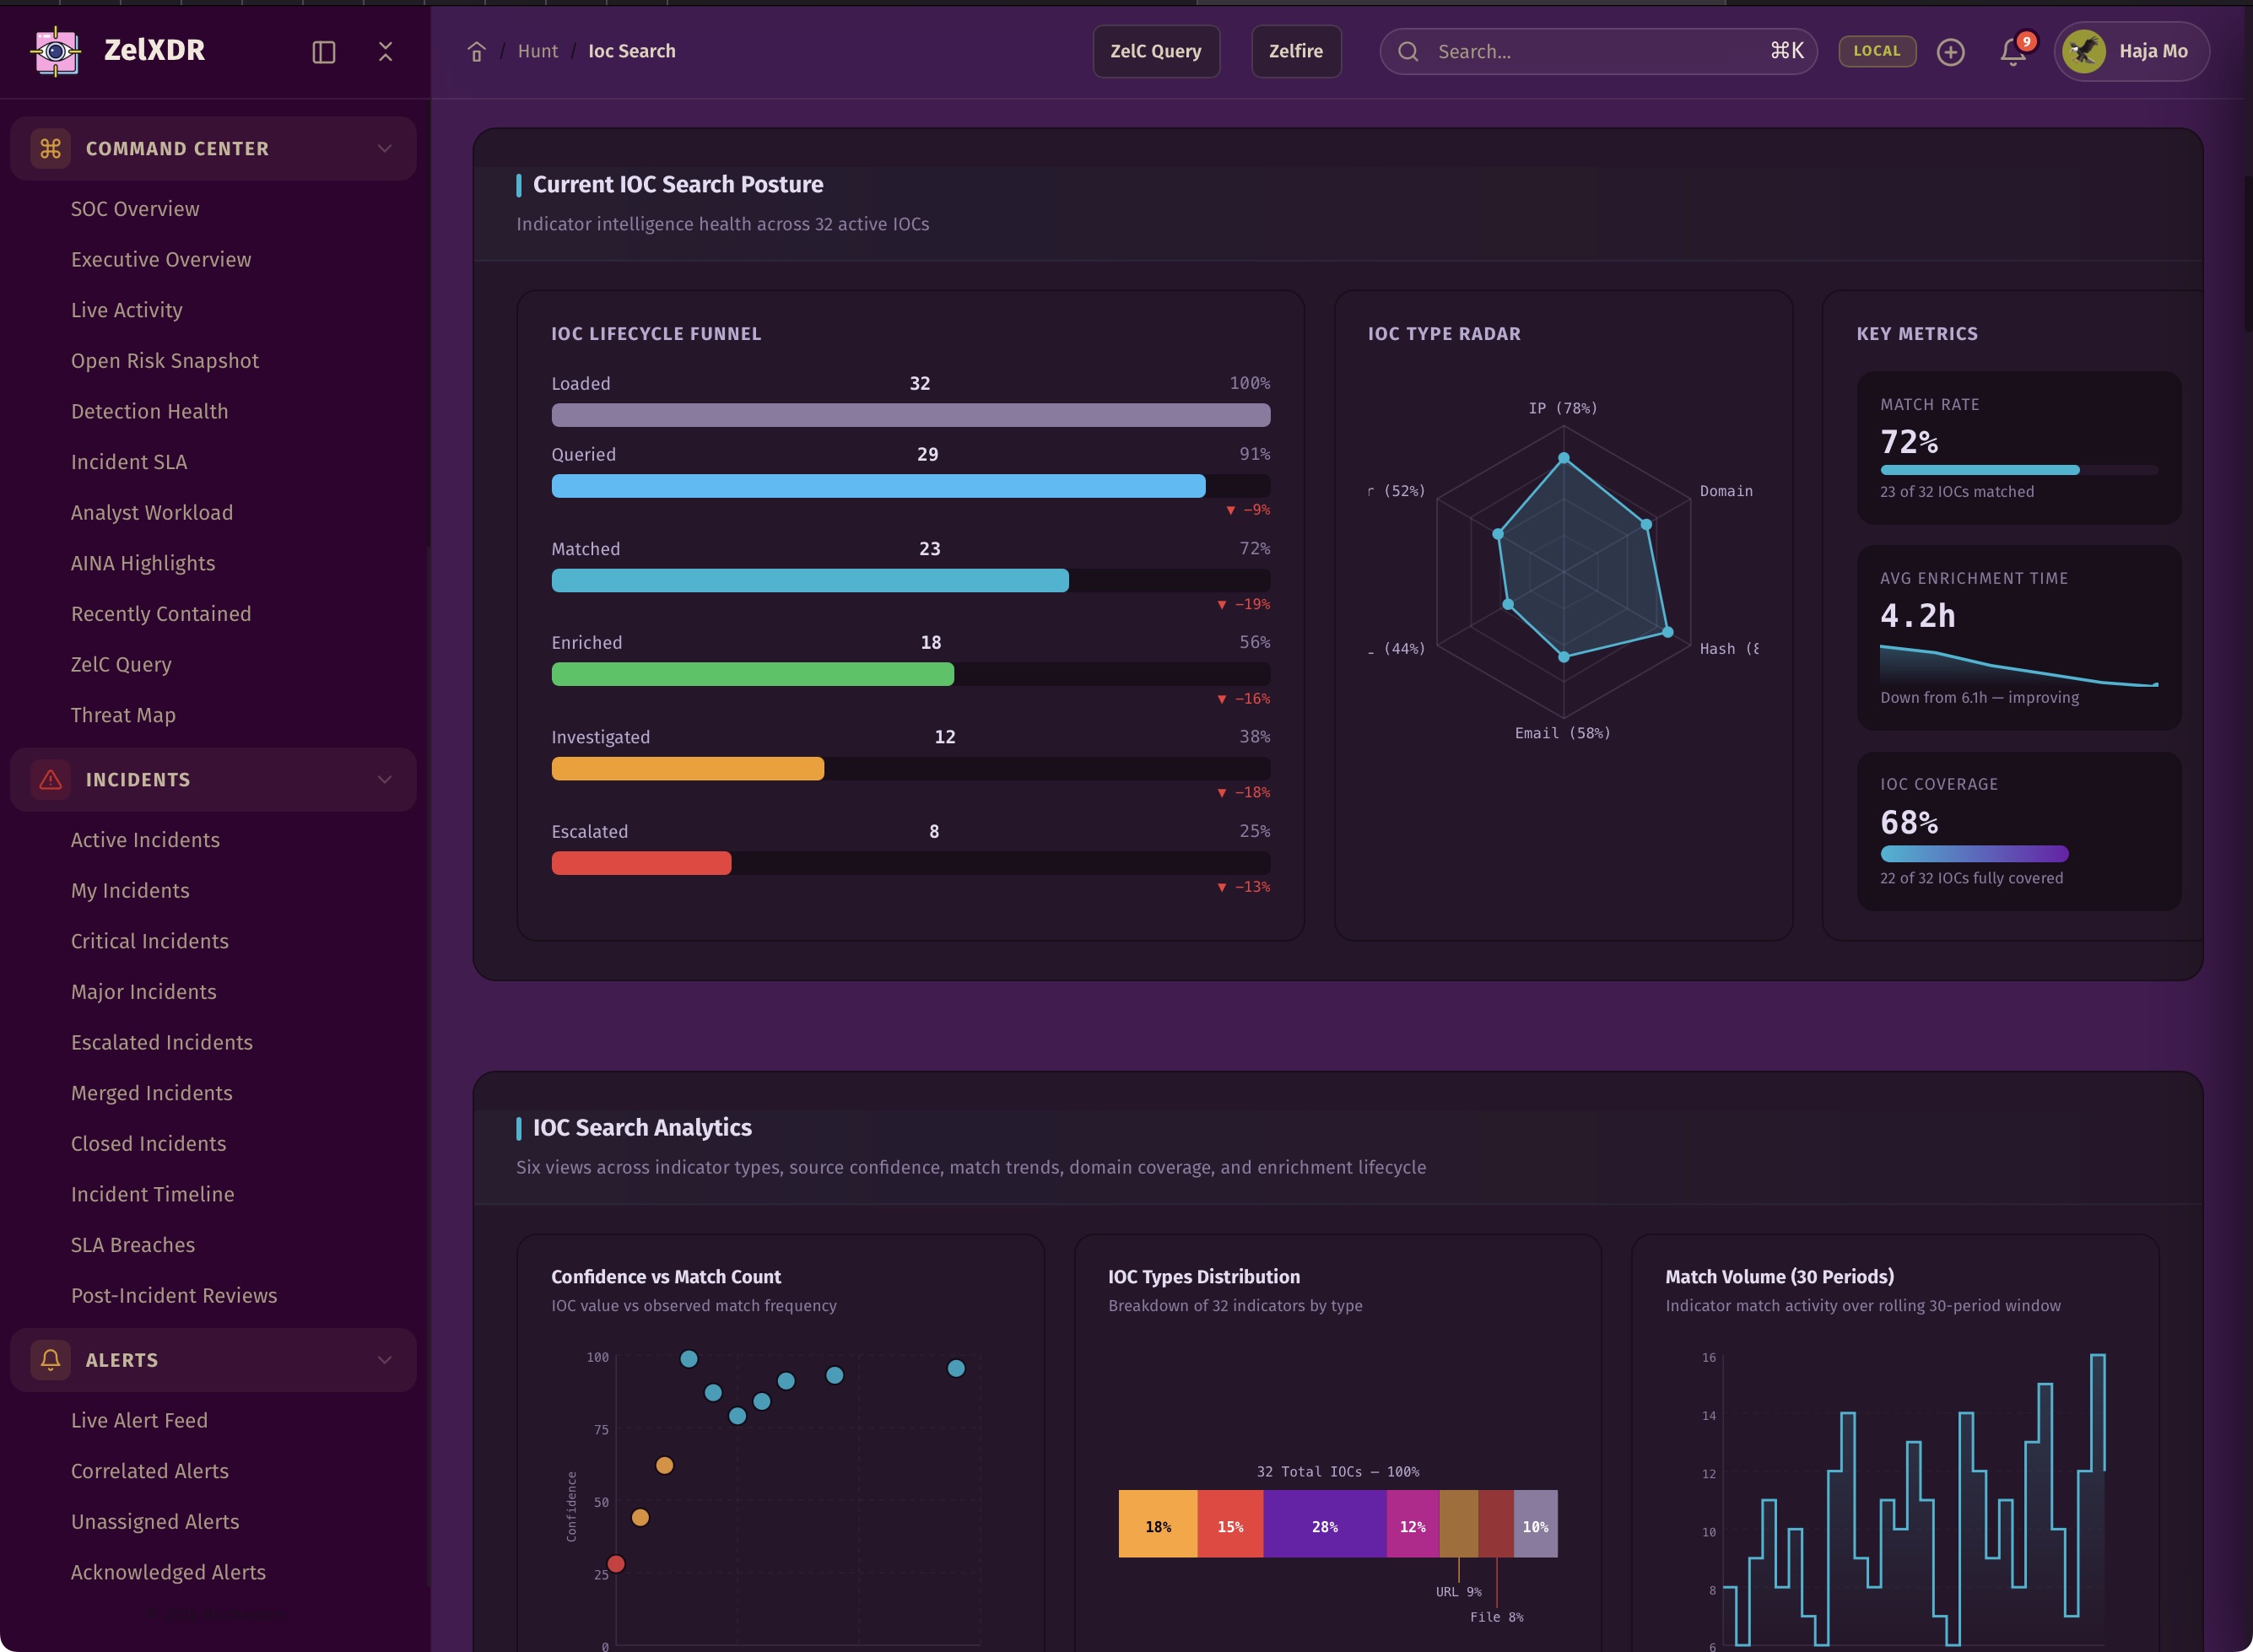
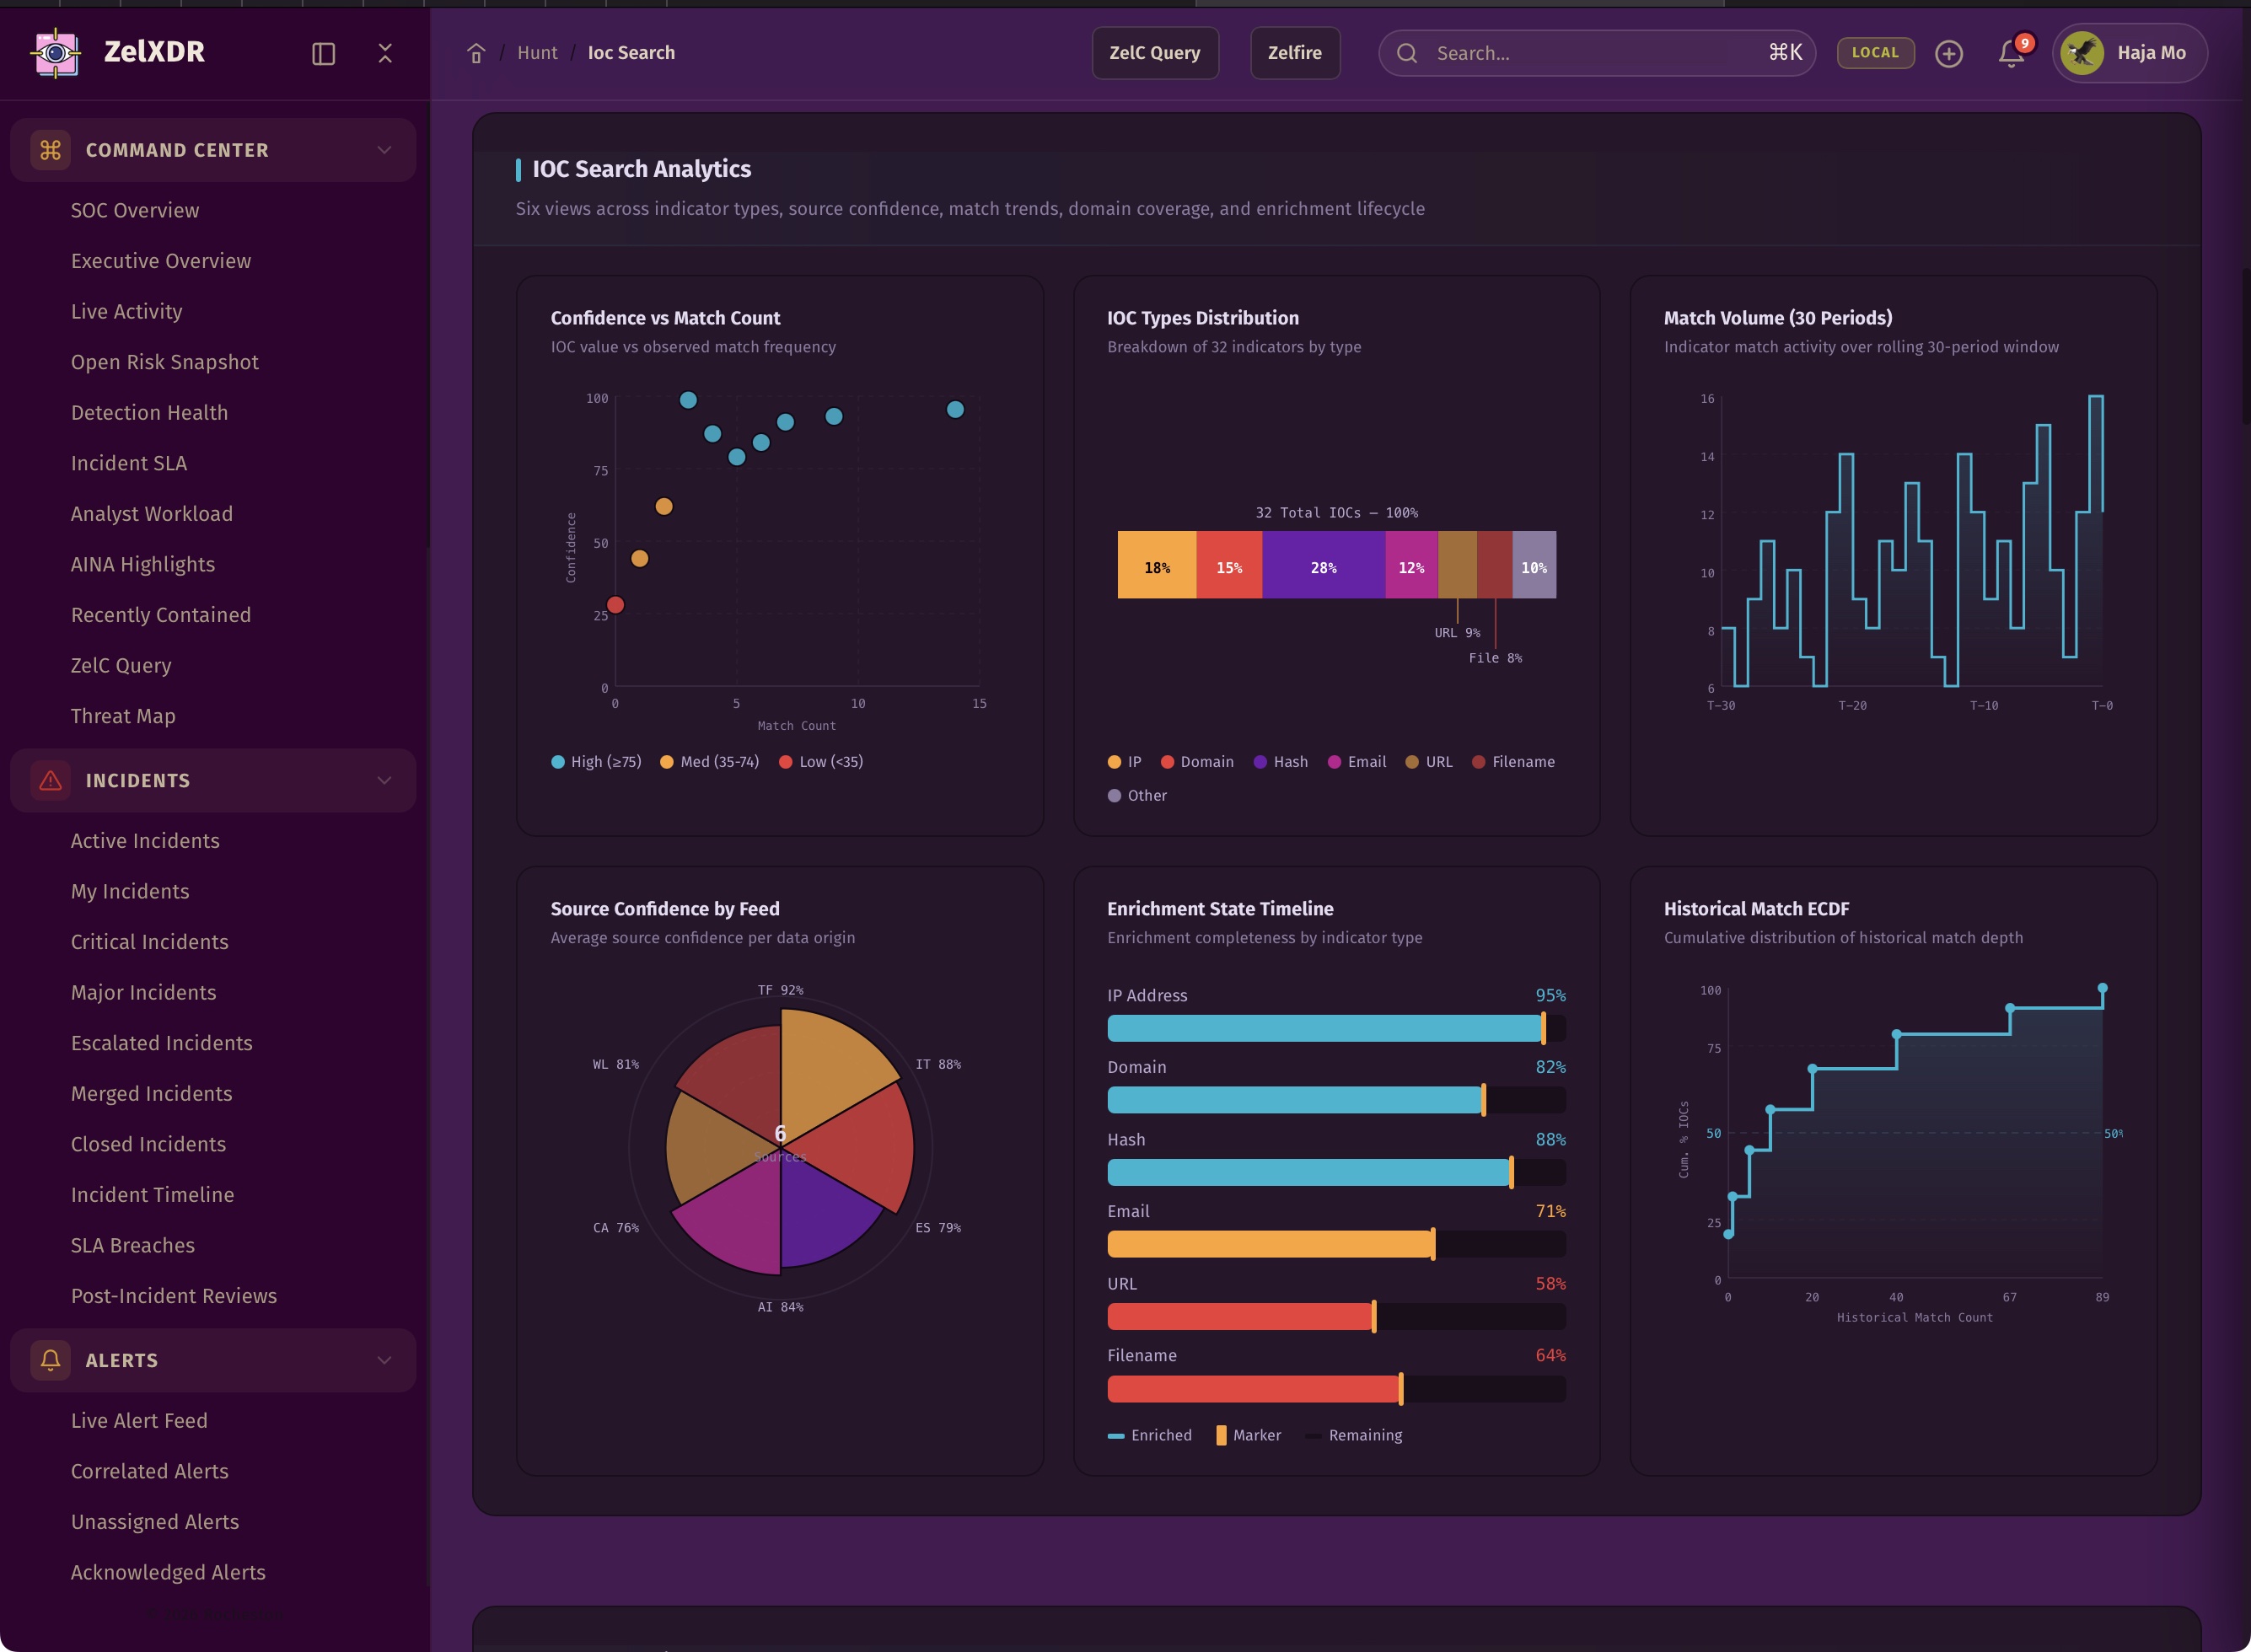
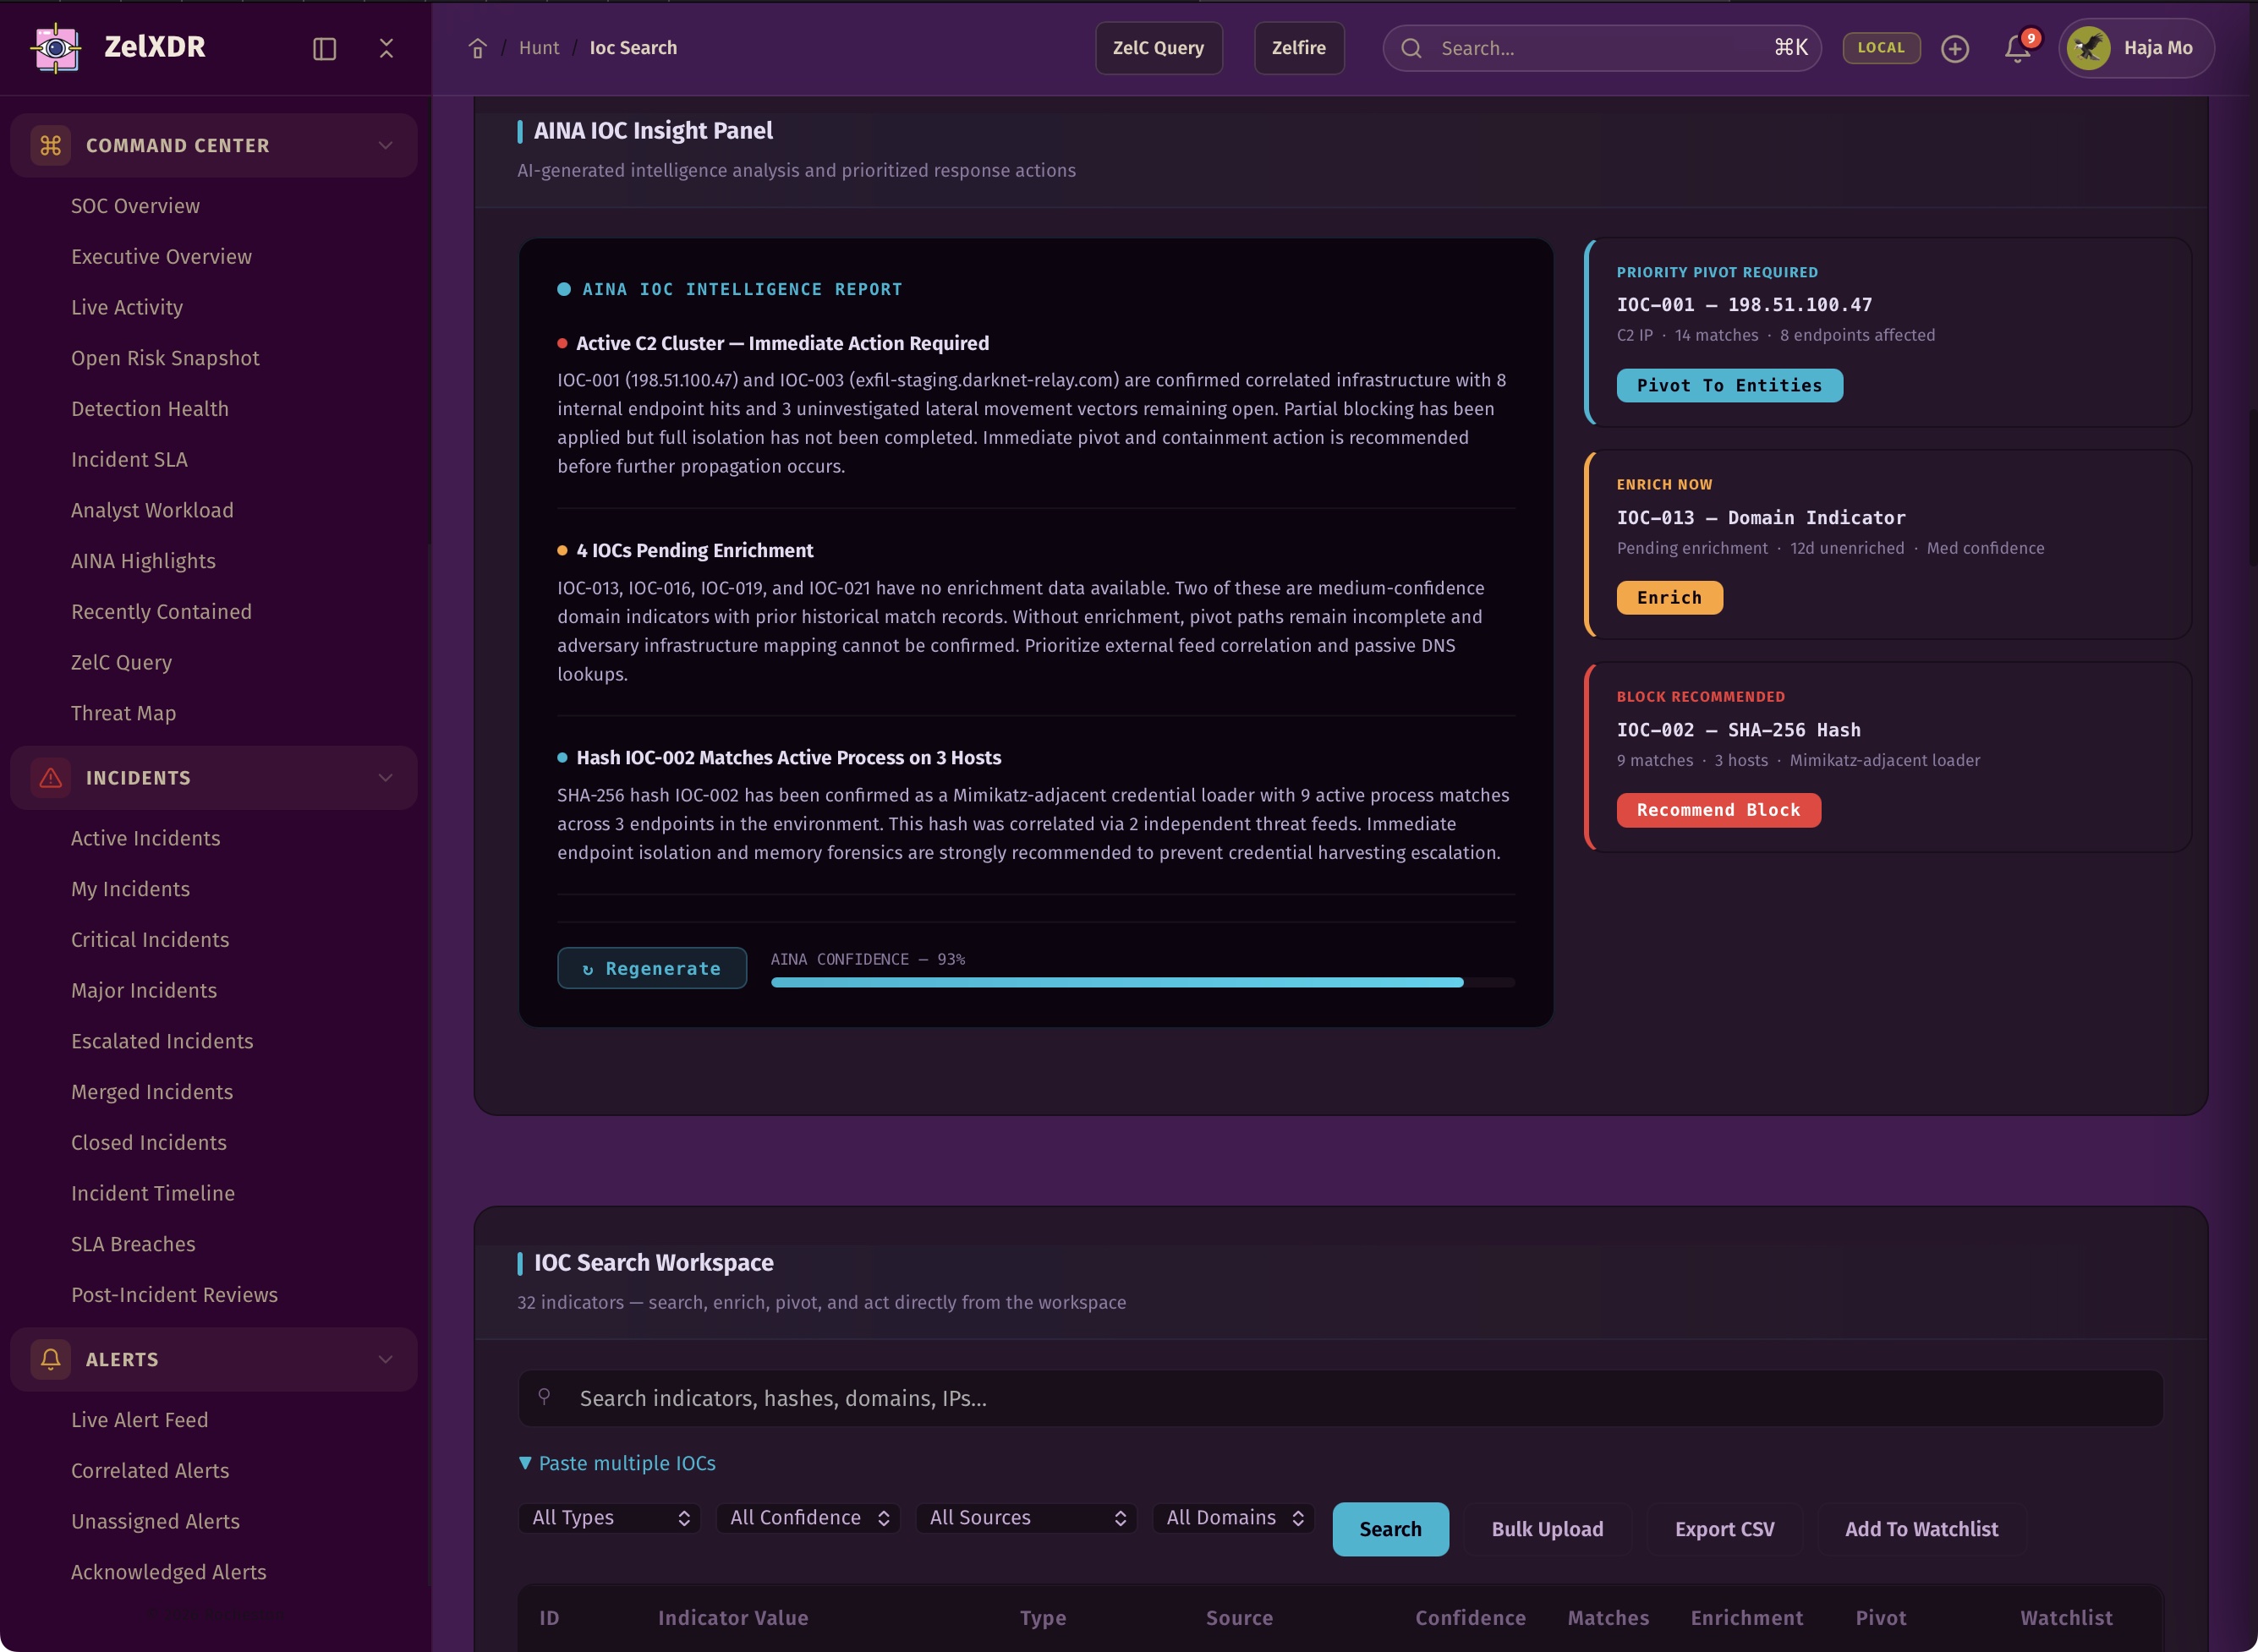
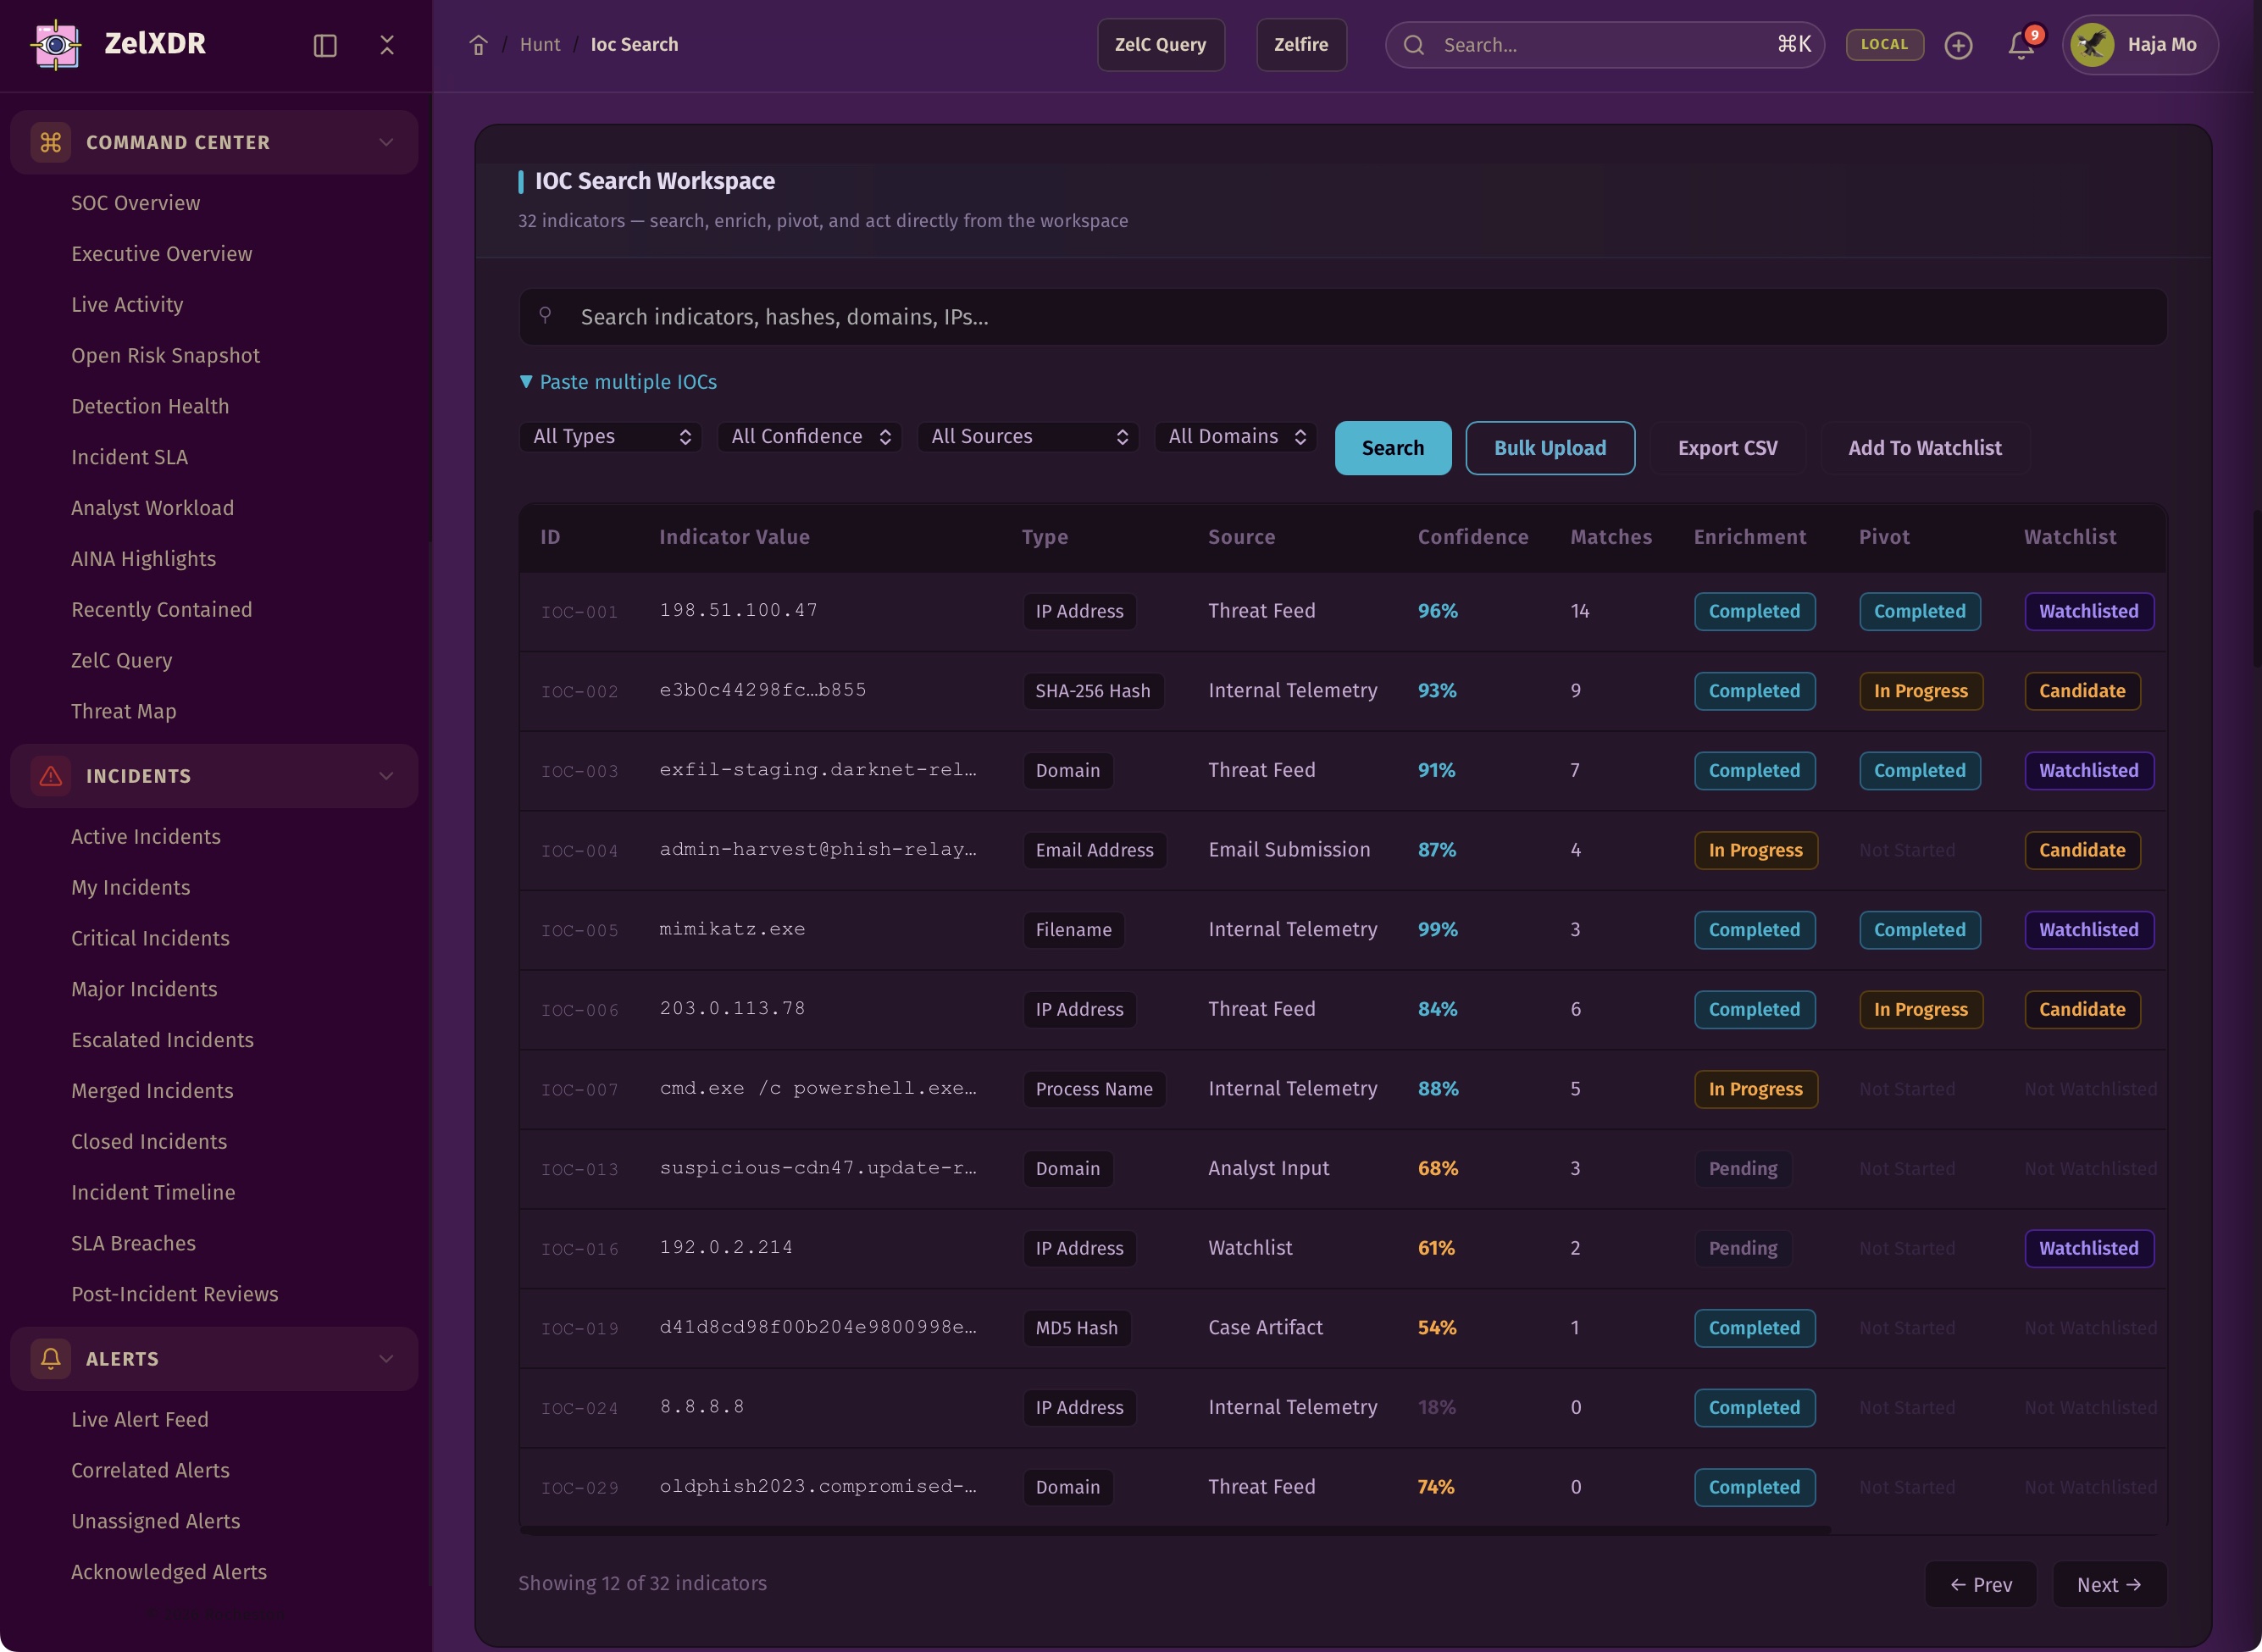
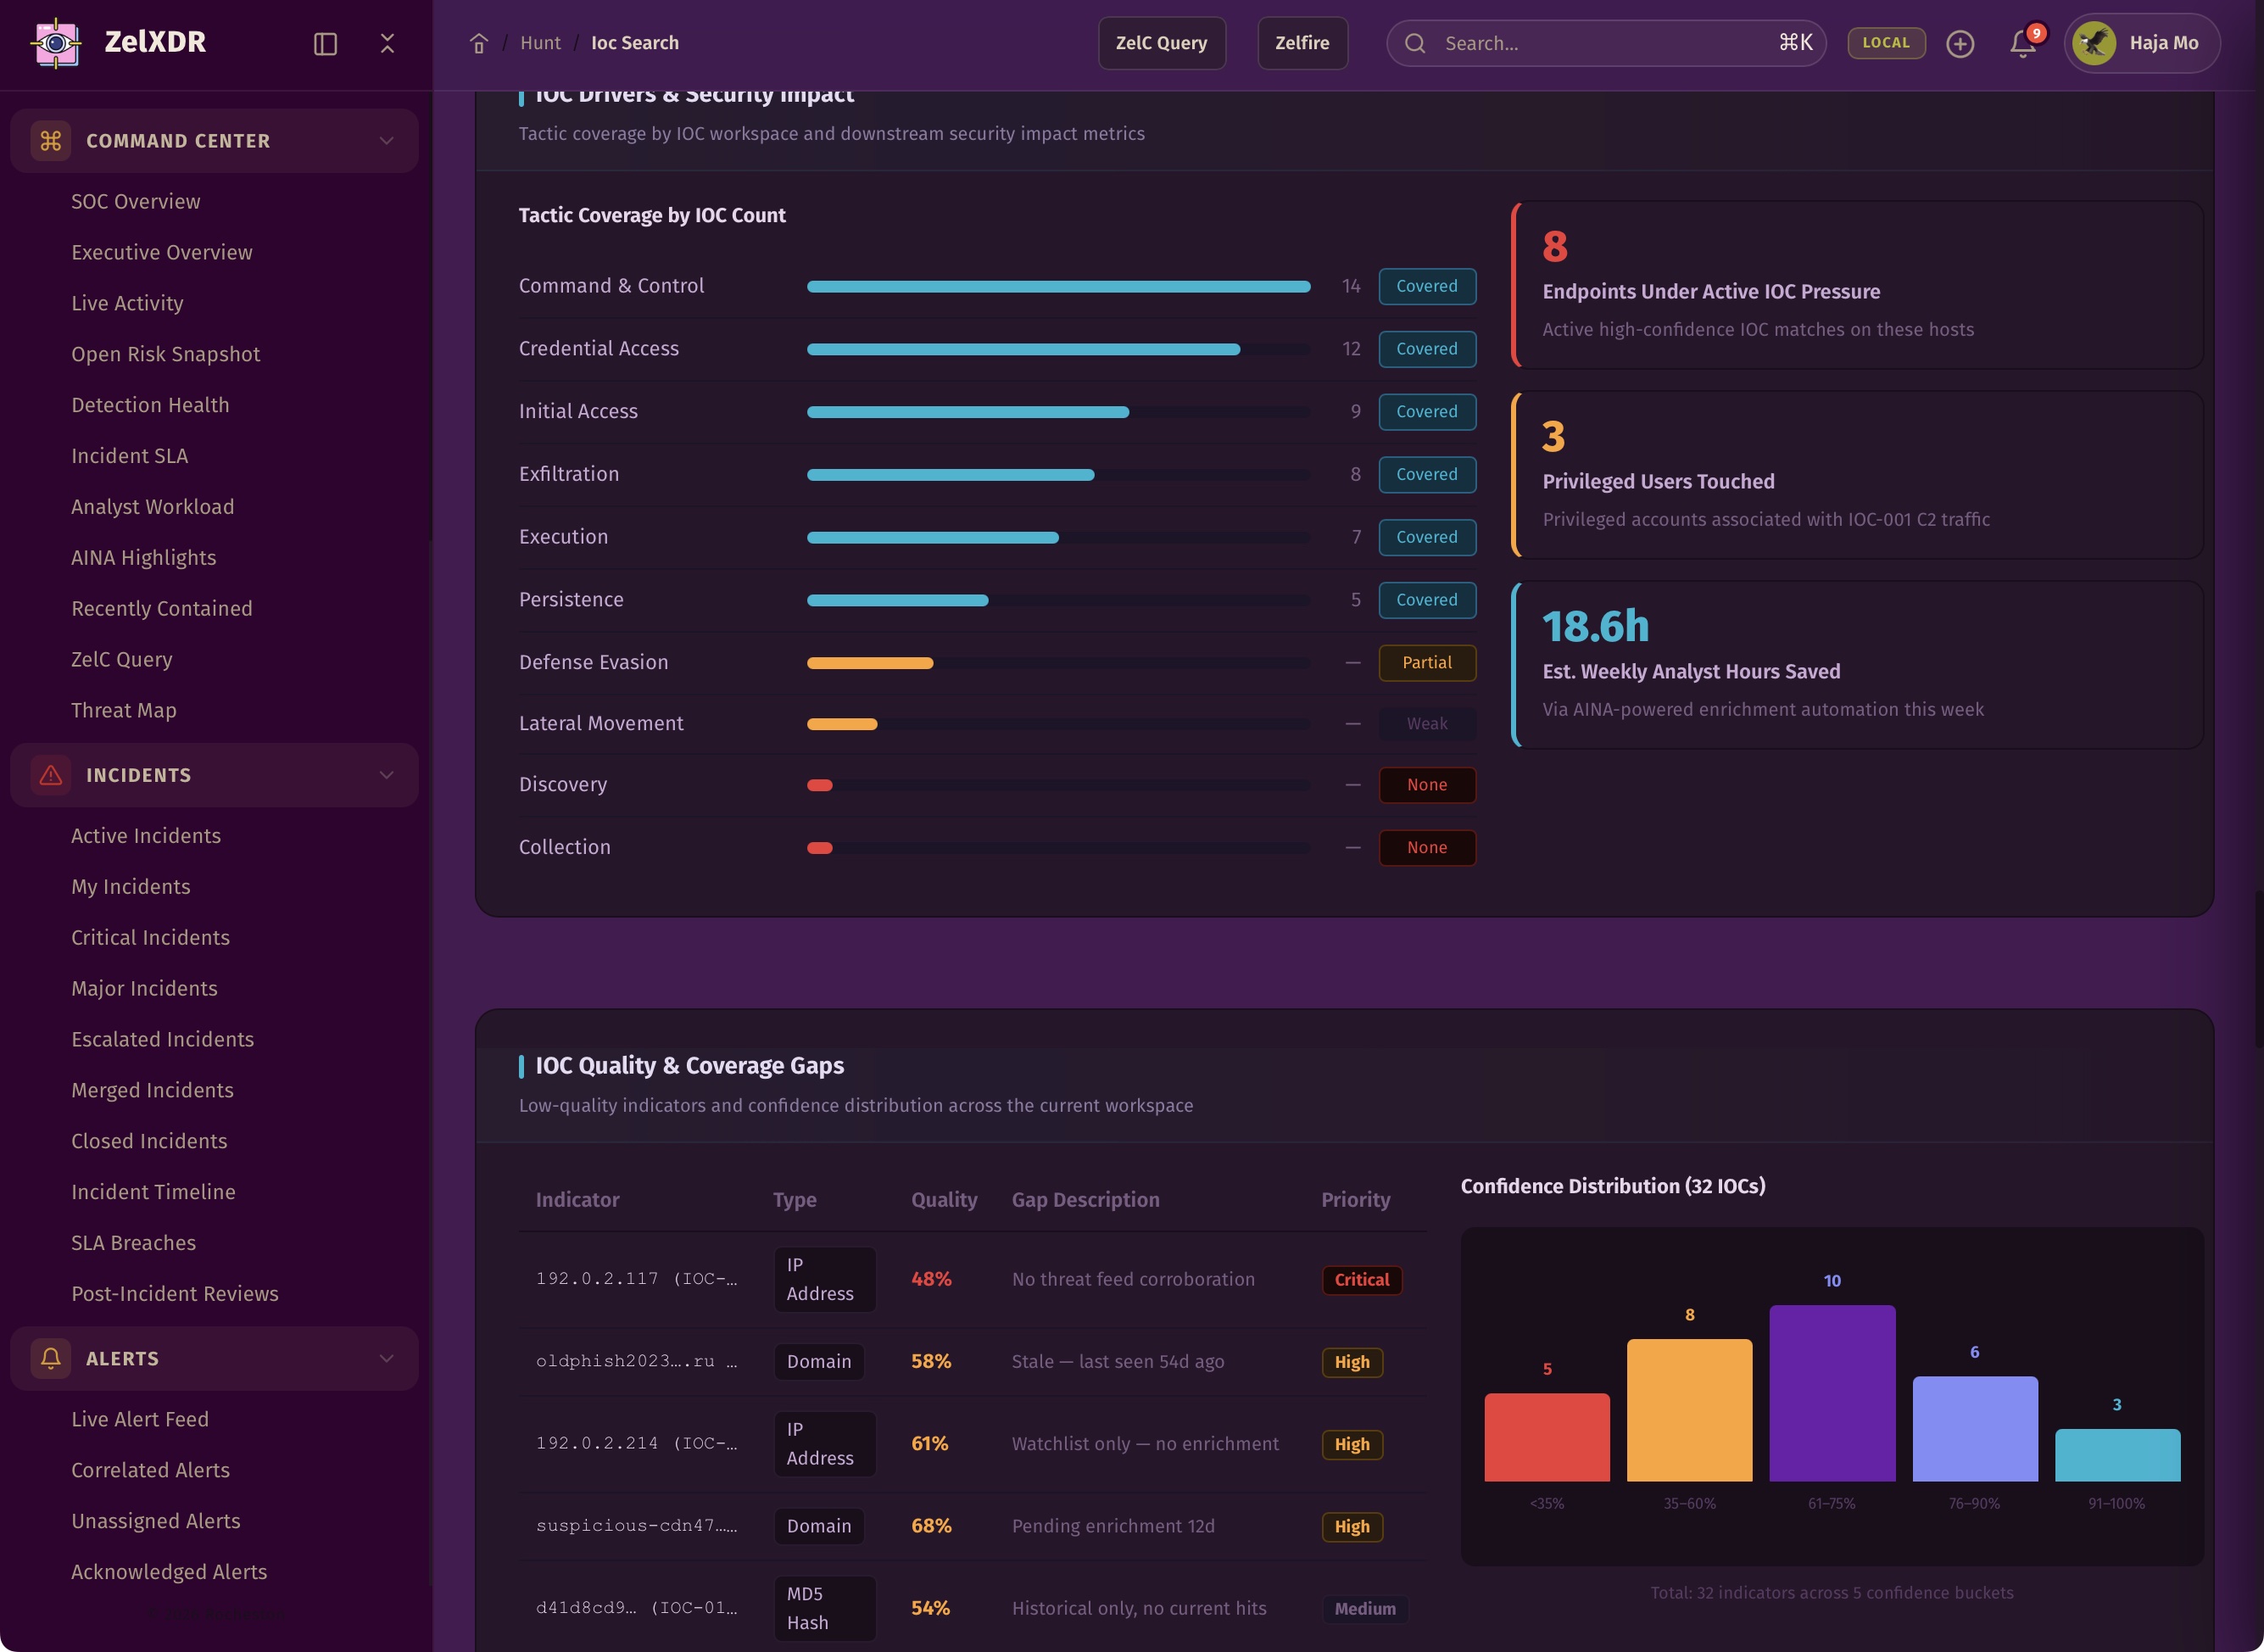
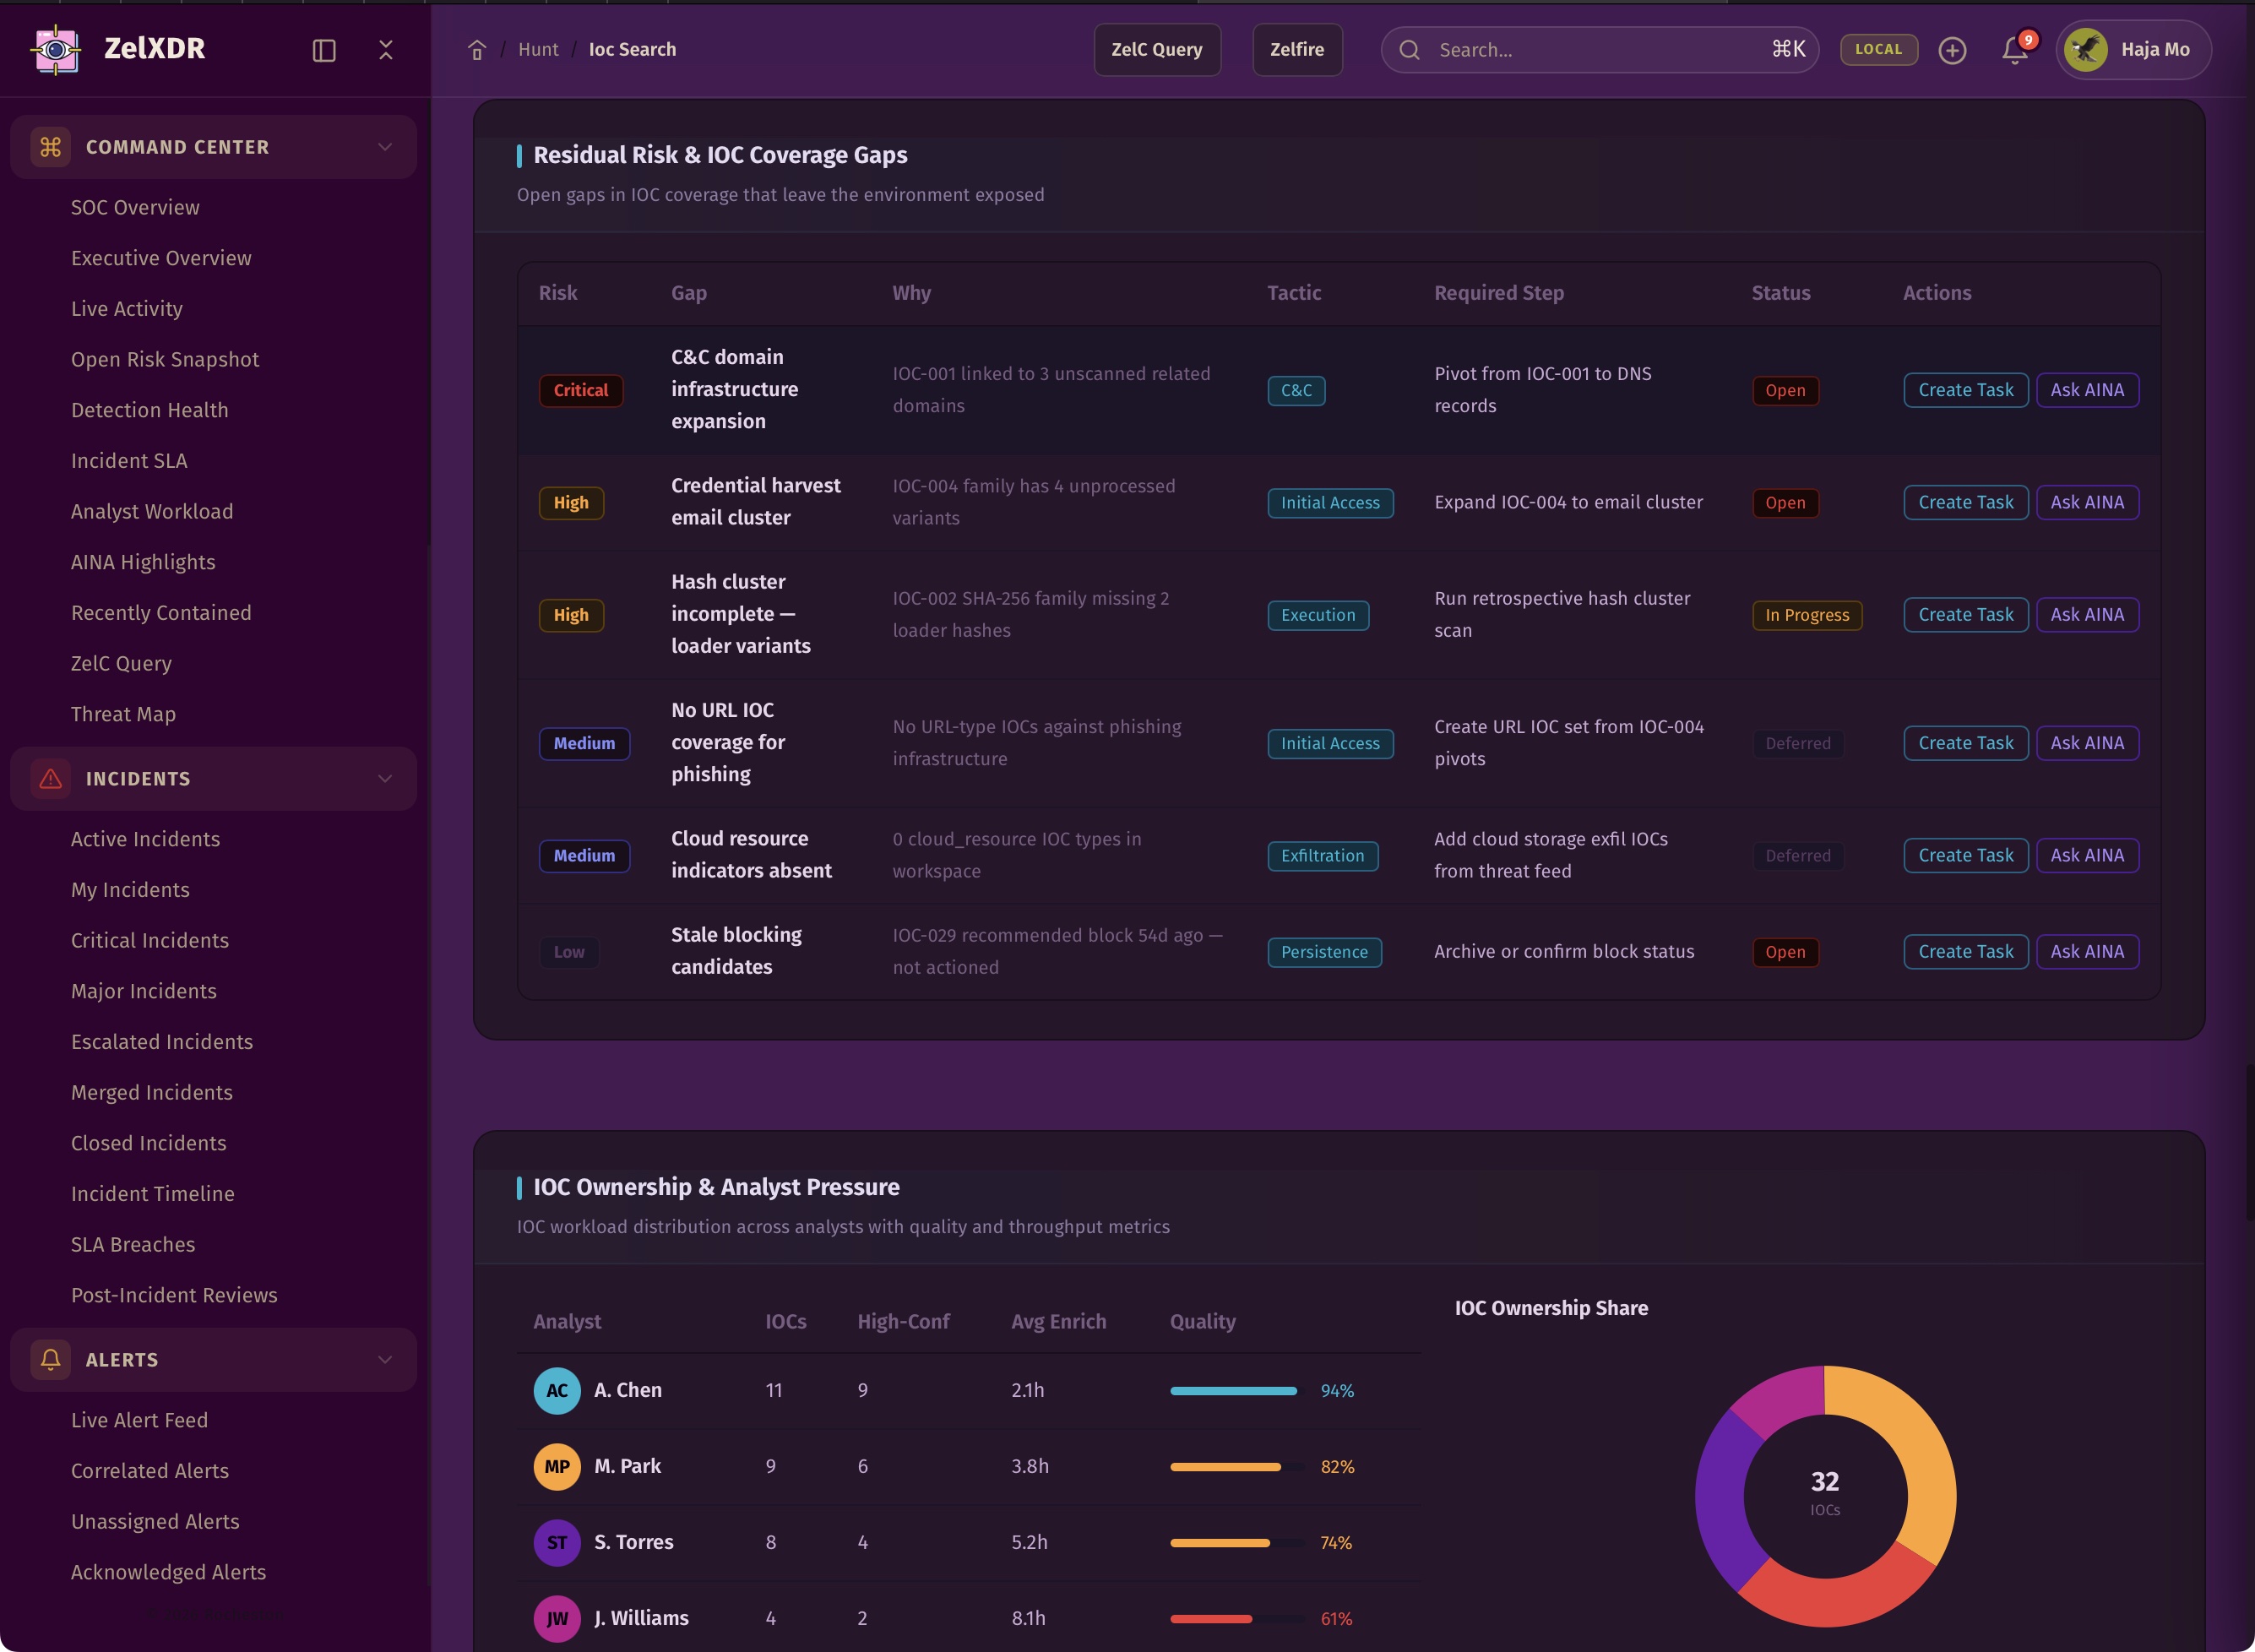
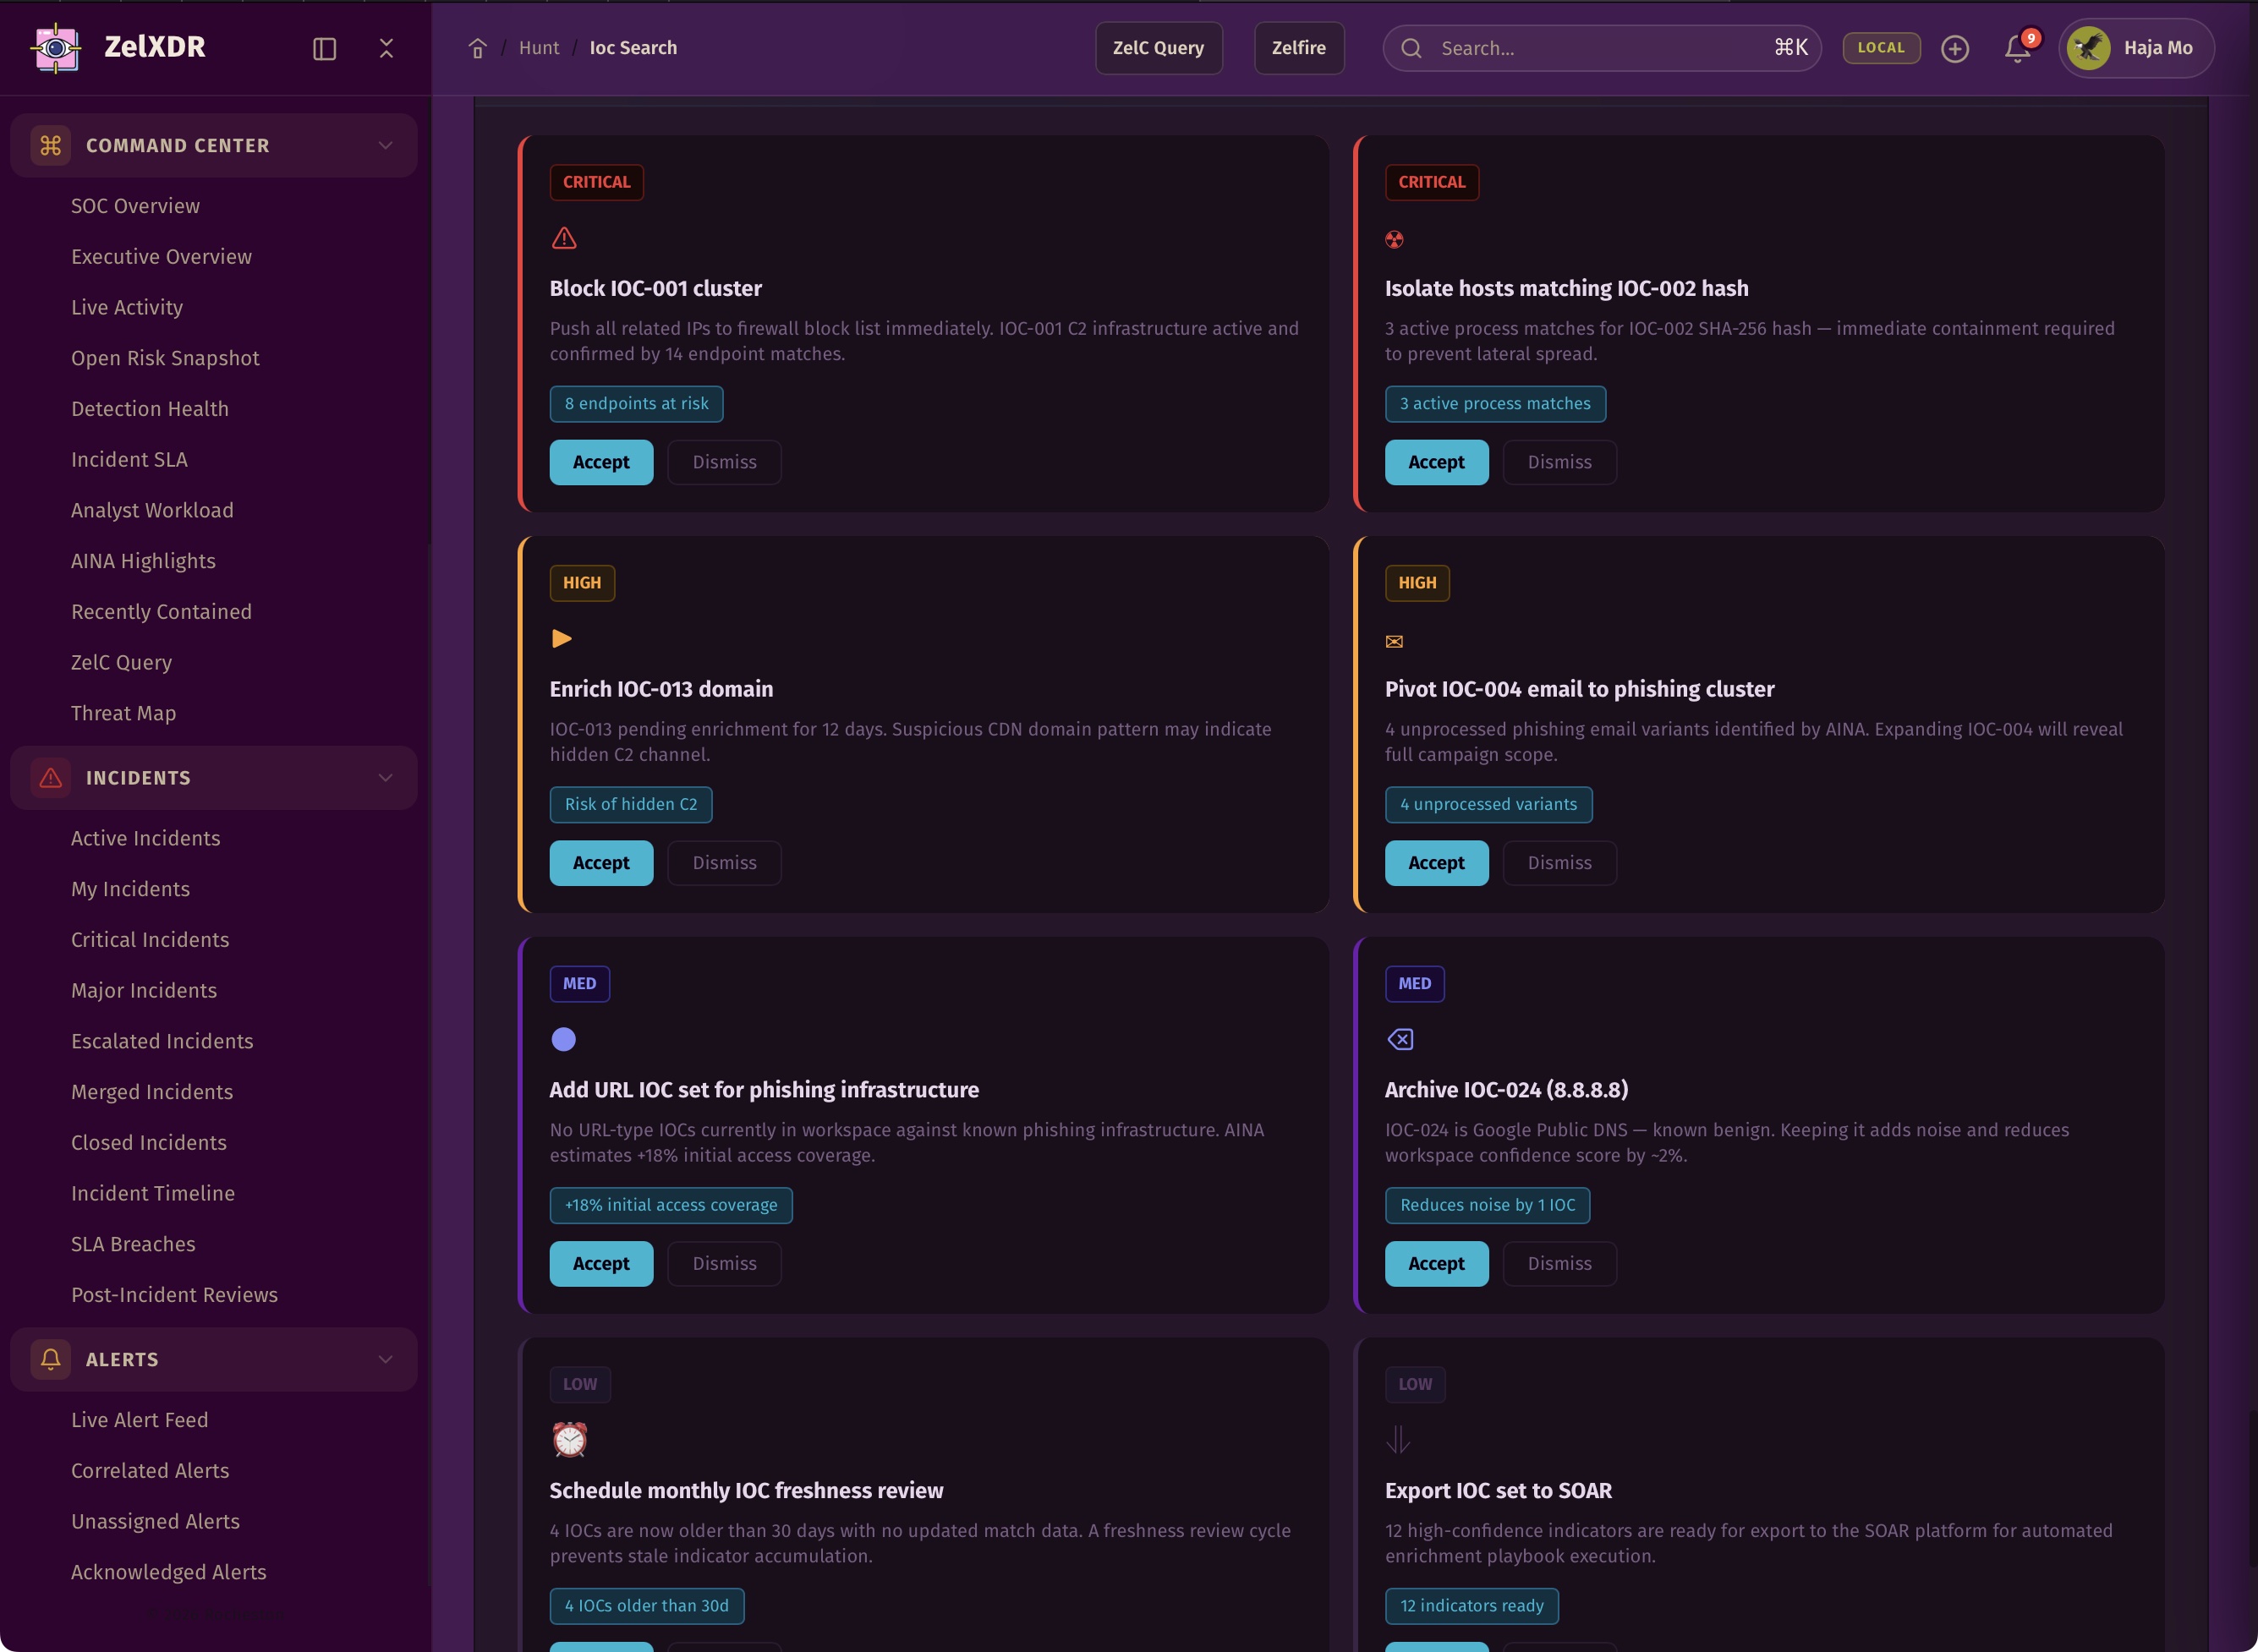
ZelXDR lets analysts search and enrich IPs, domains, hashes, URLs, emails, and other indicators across internal telemetry and external intelligence, then pivot them into meaningful investigations.
An IOC becomes valuable when it connects to real impact.
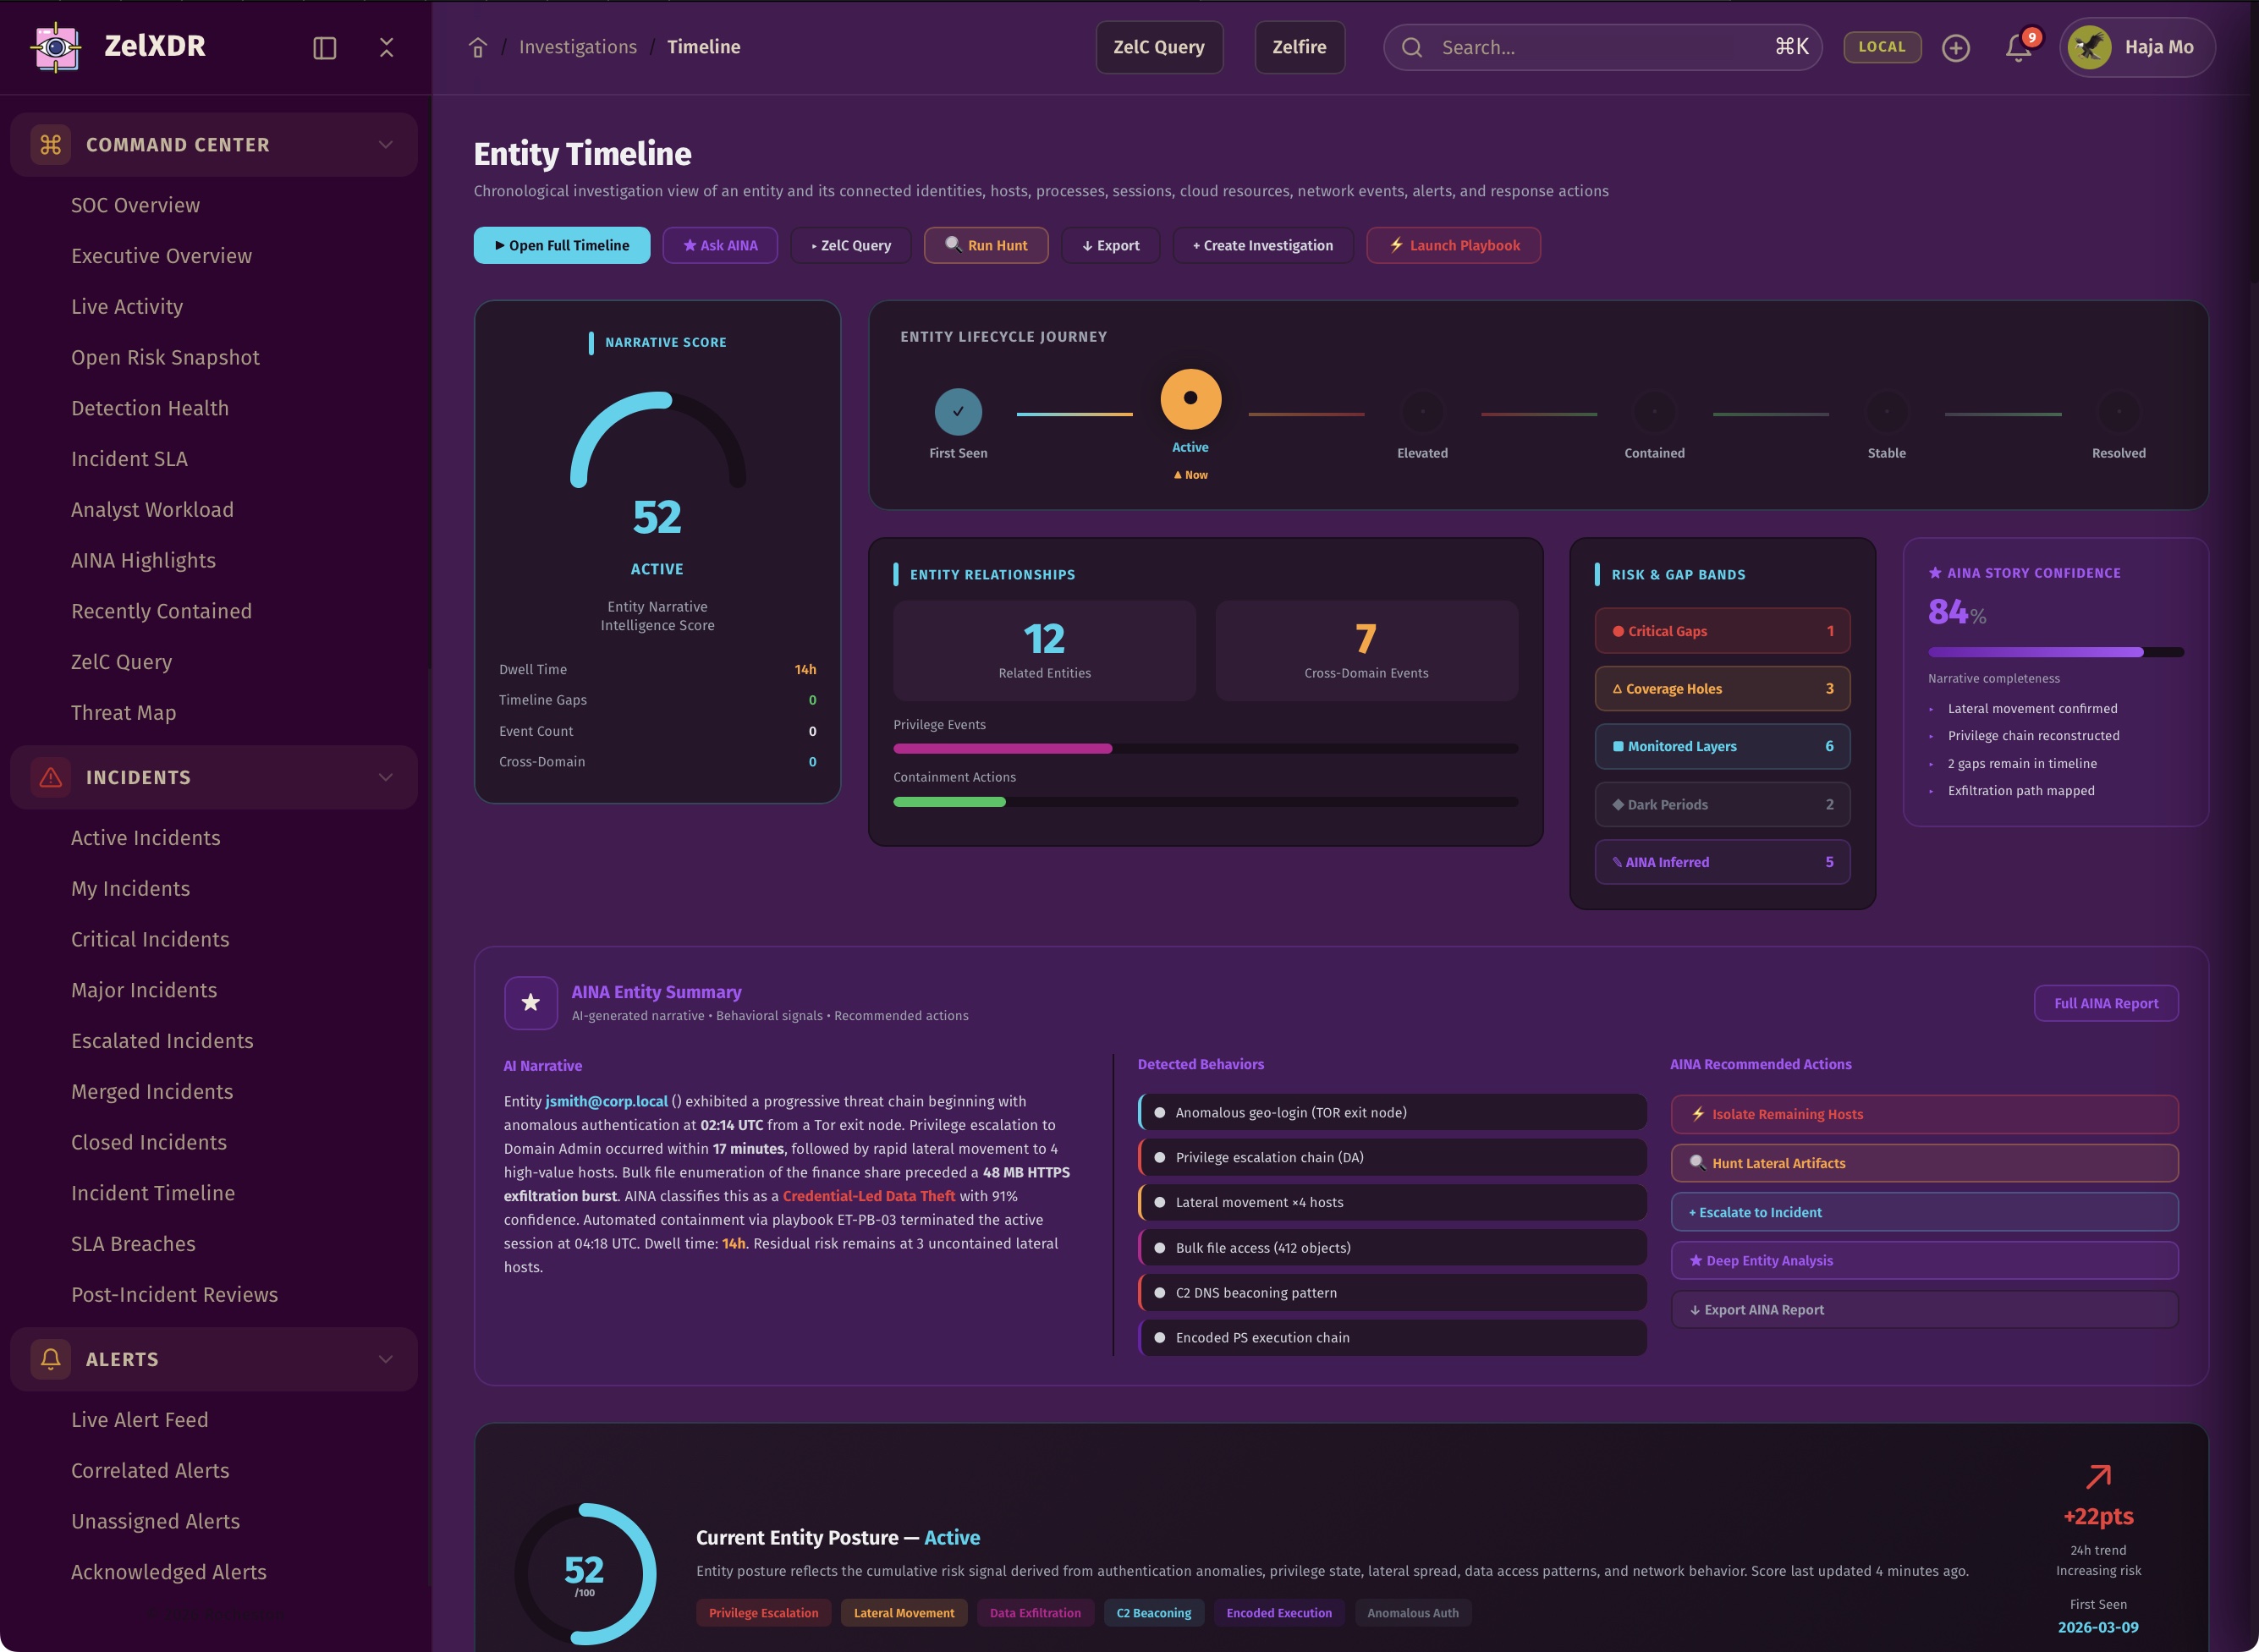
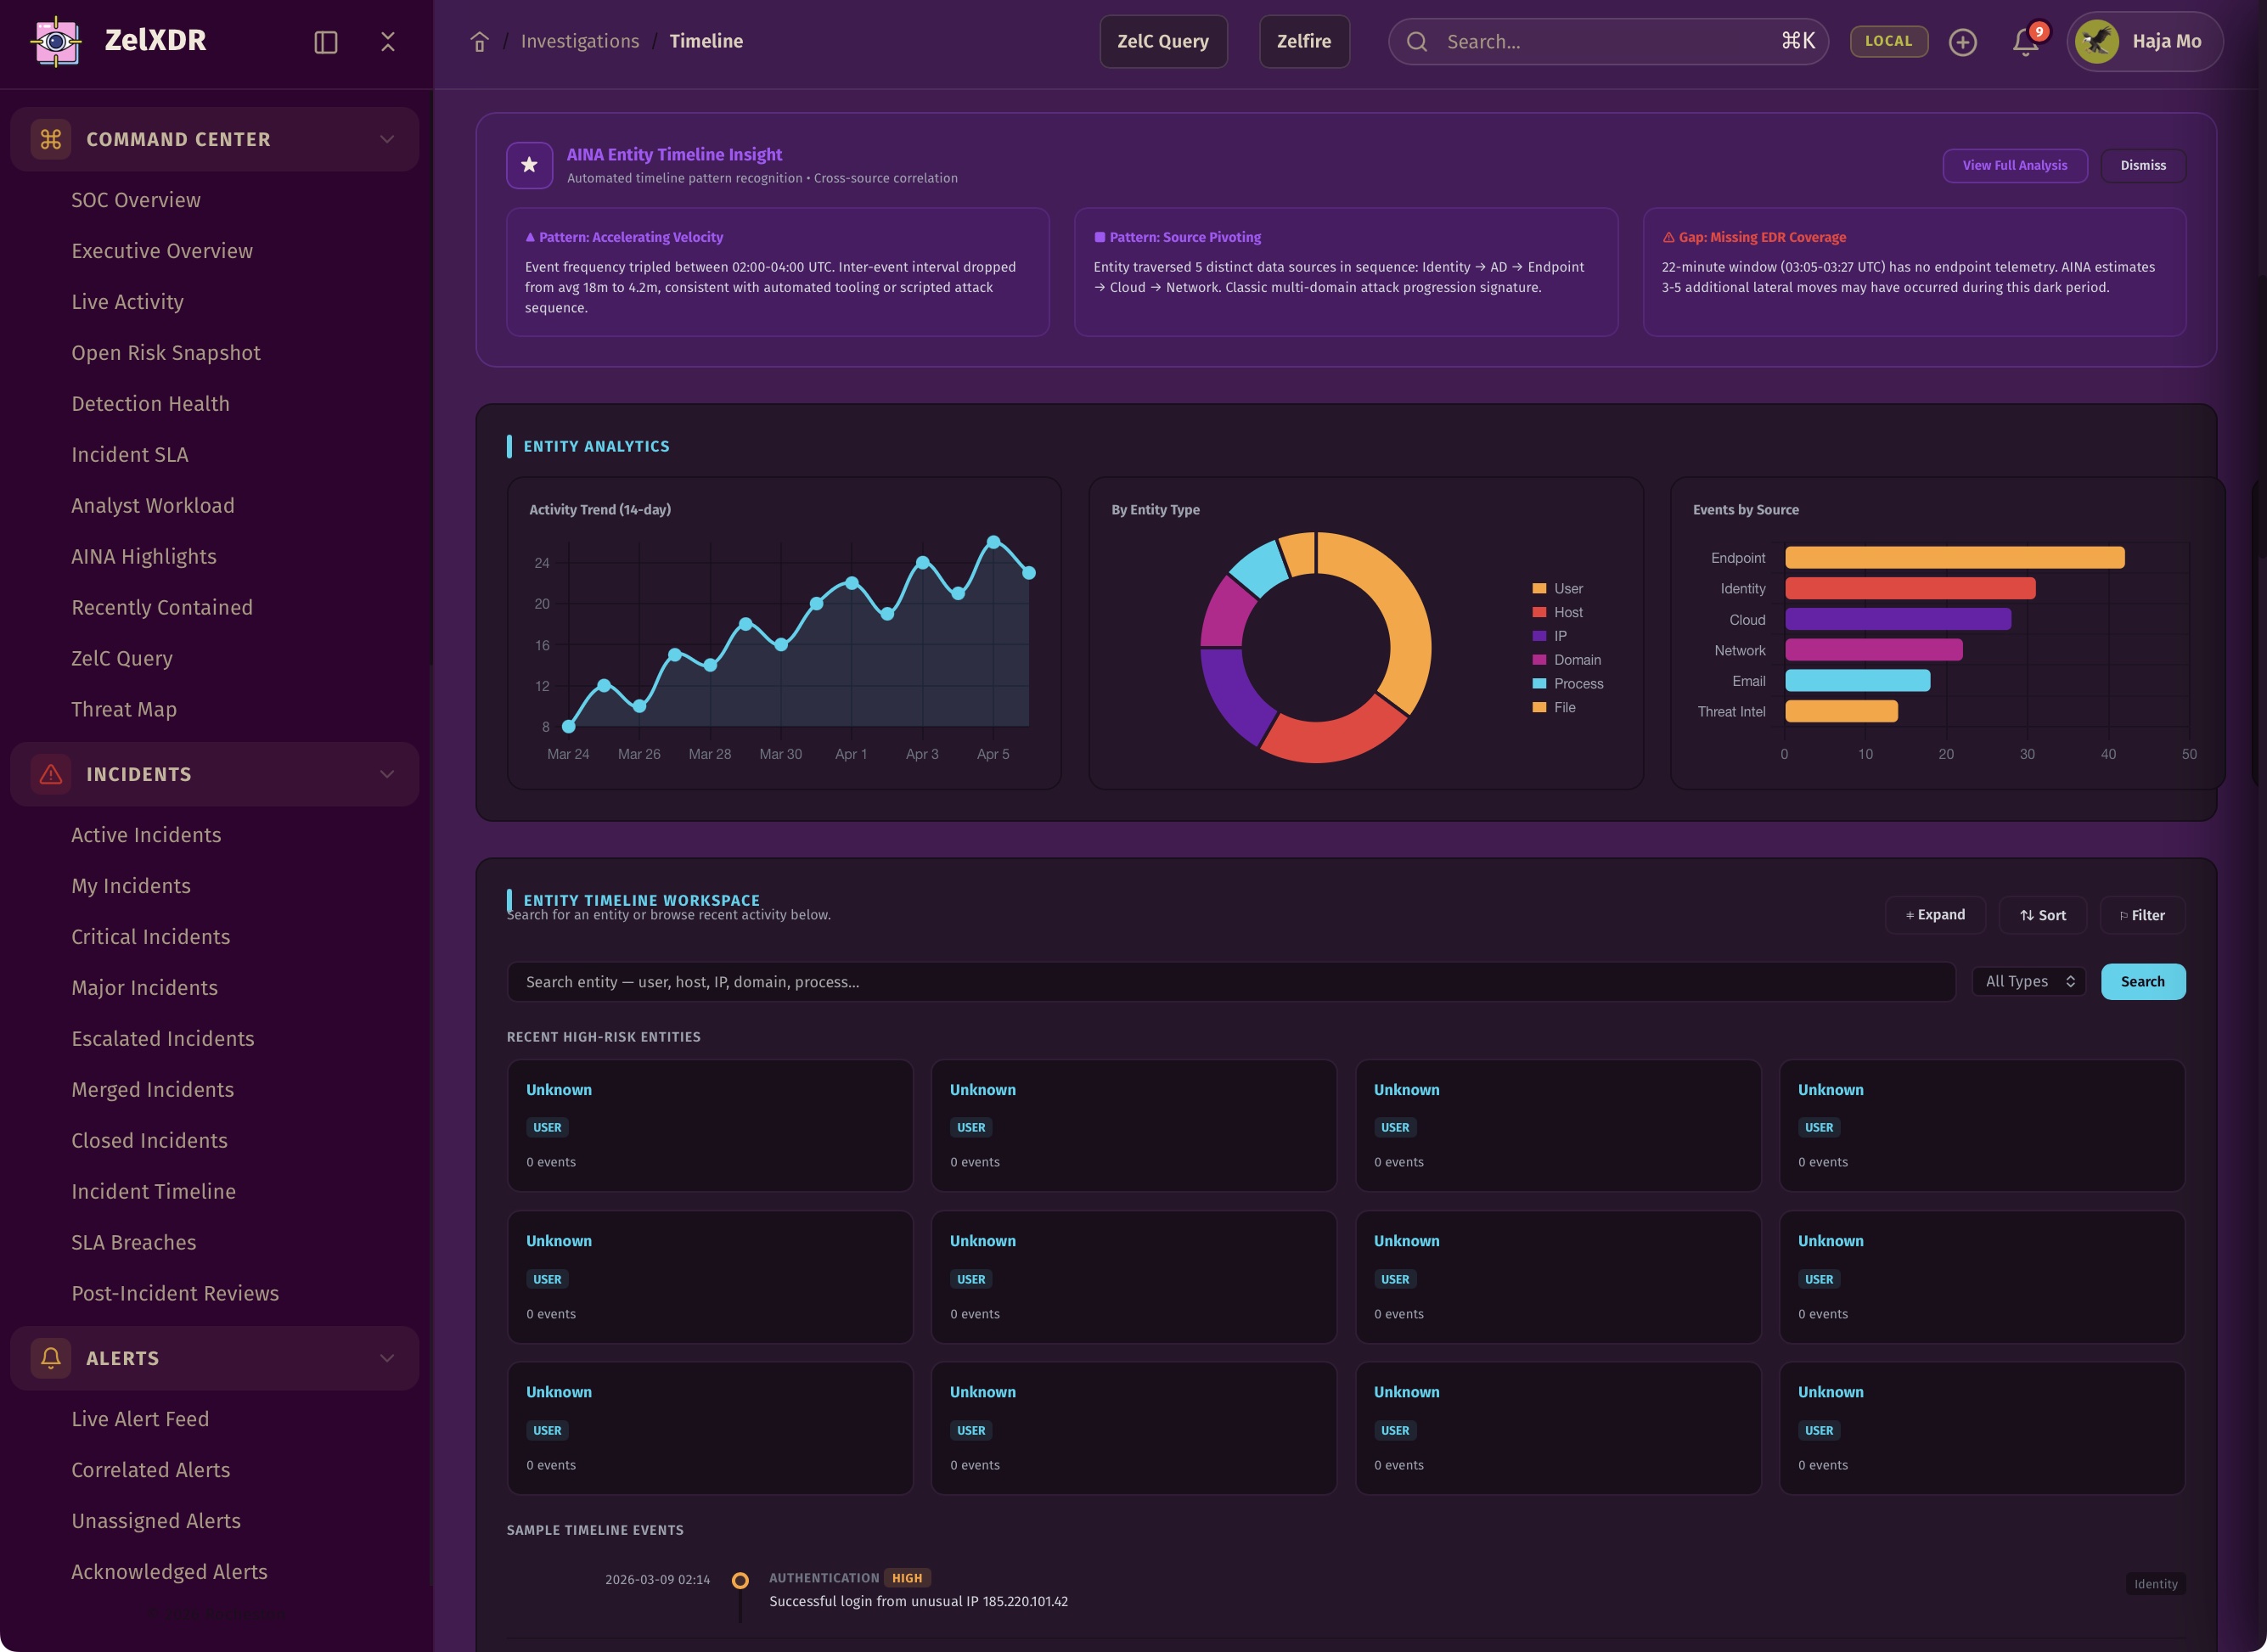
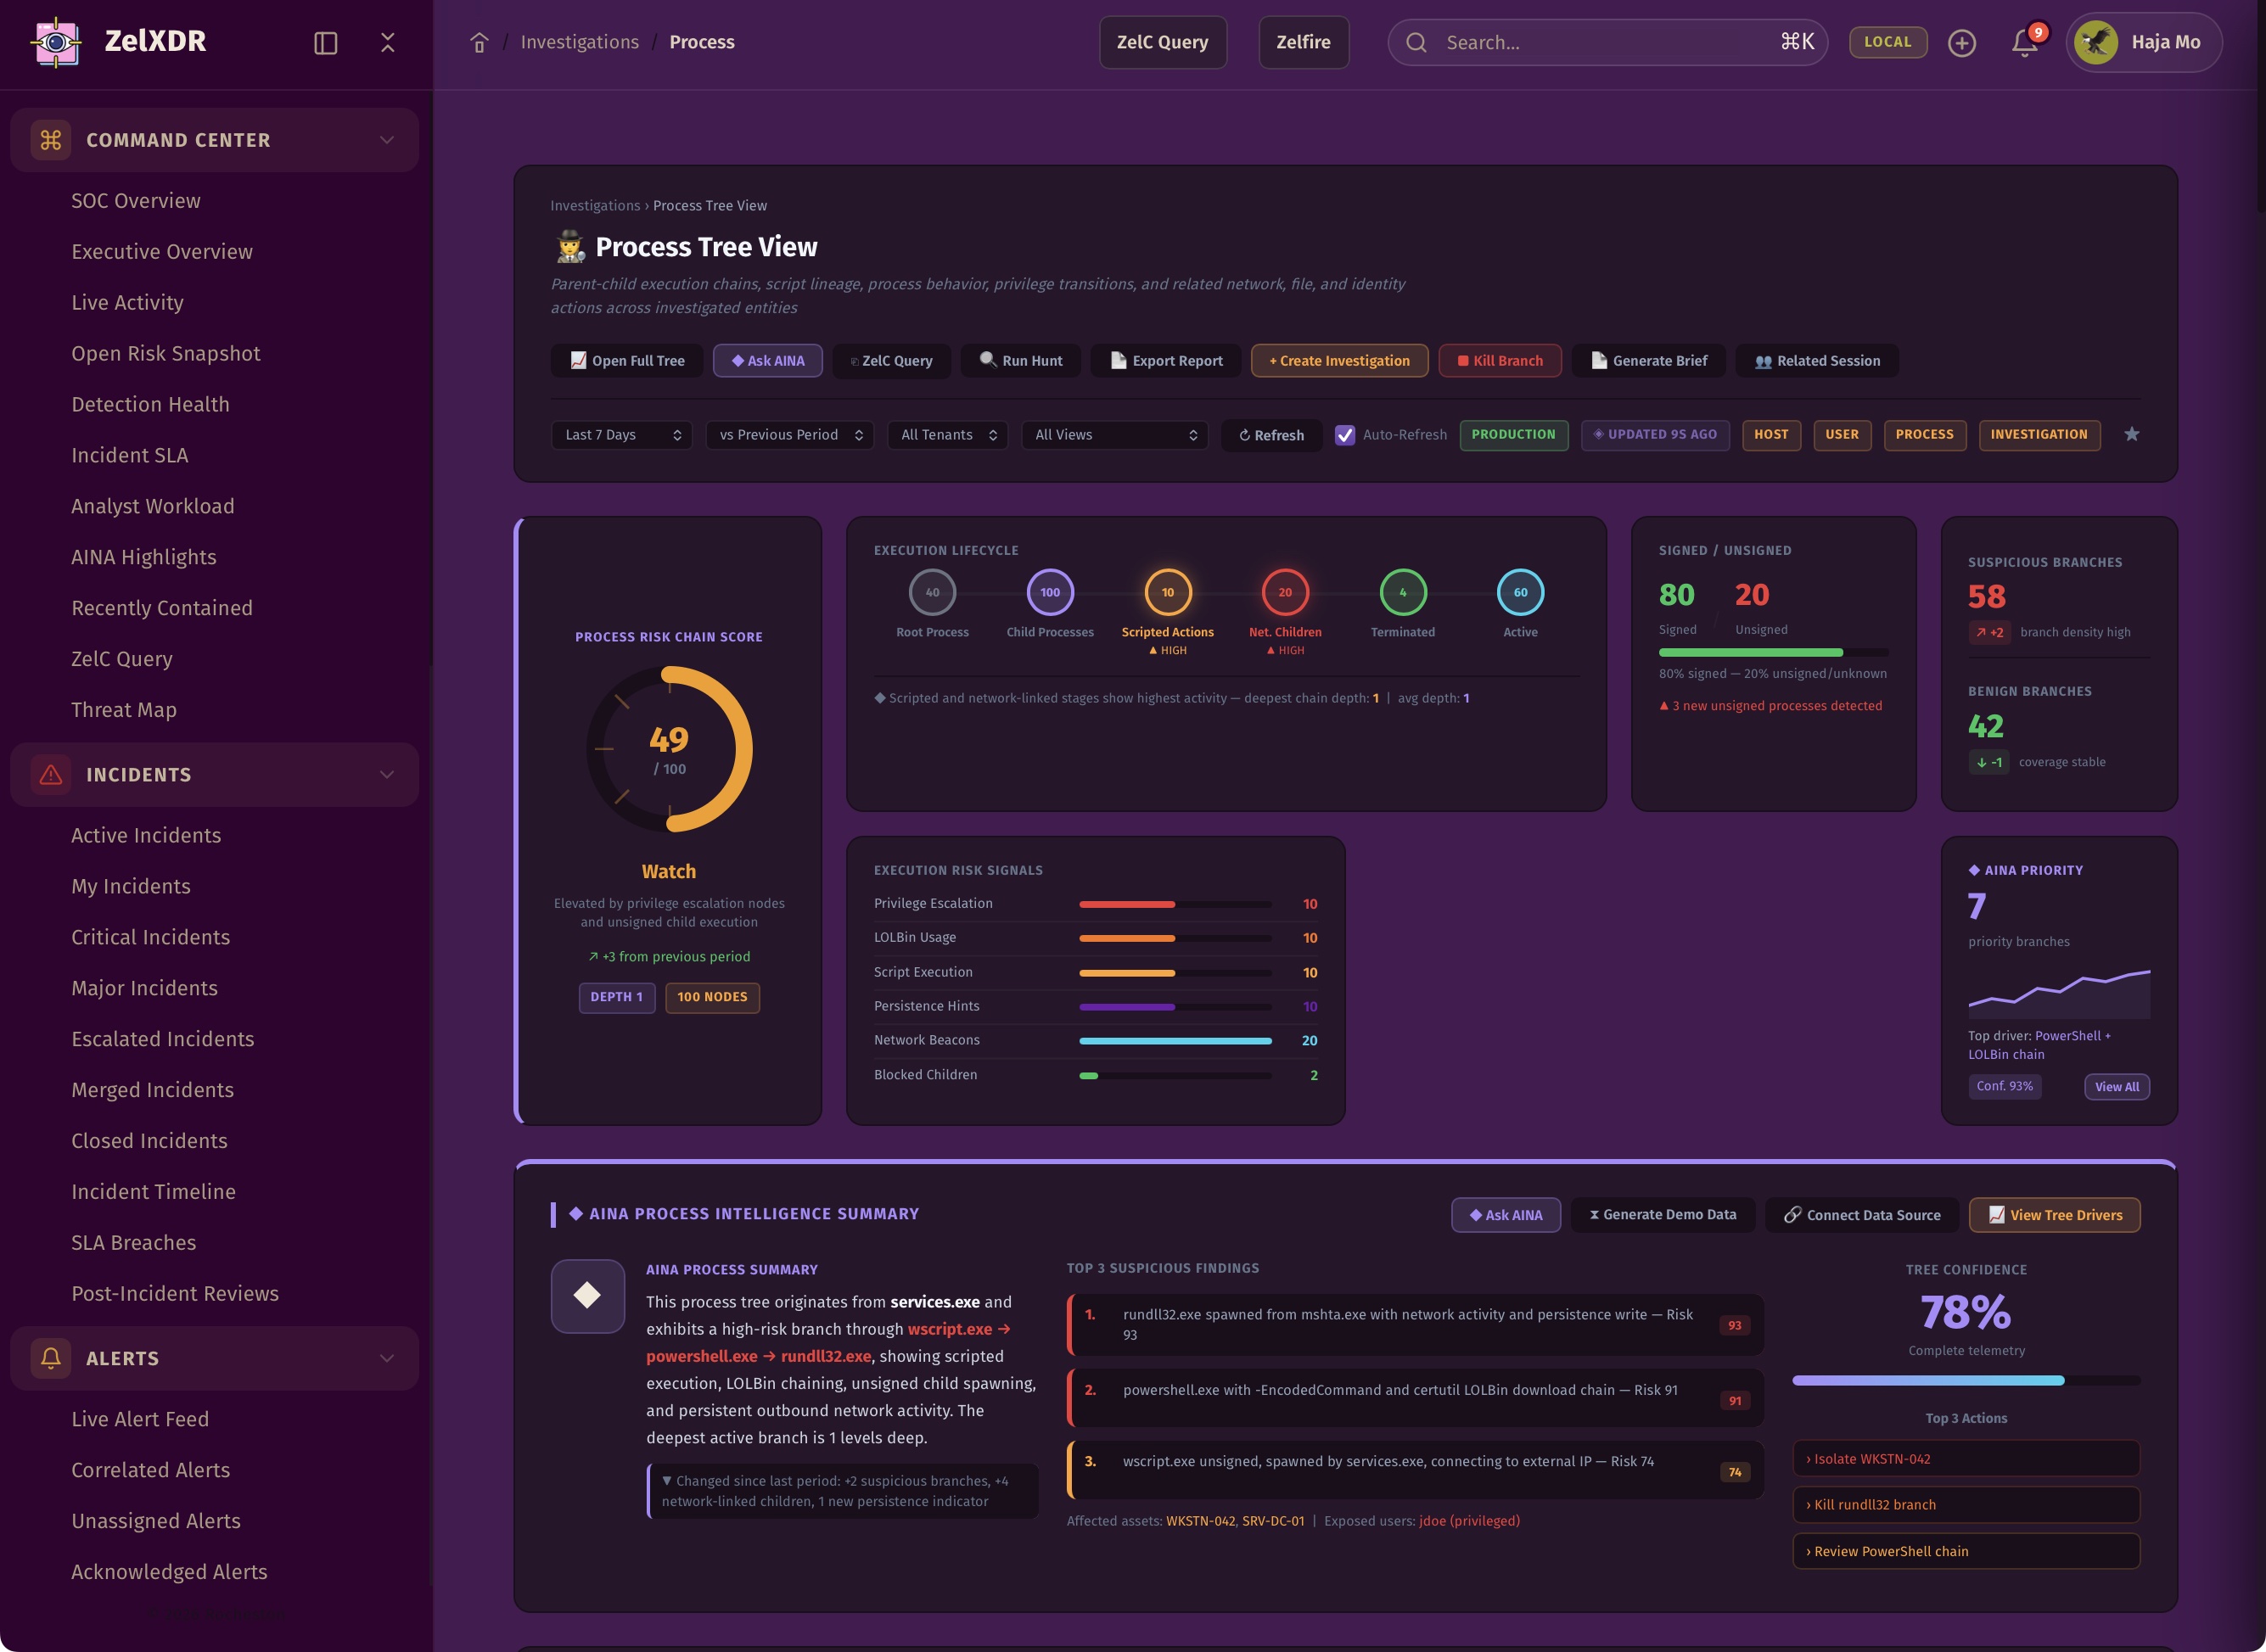
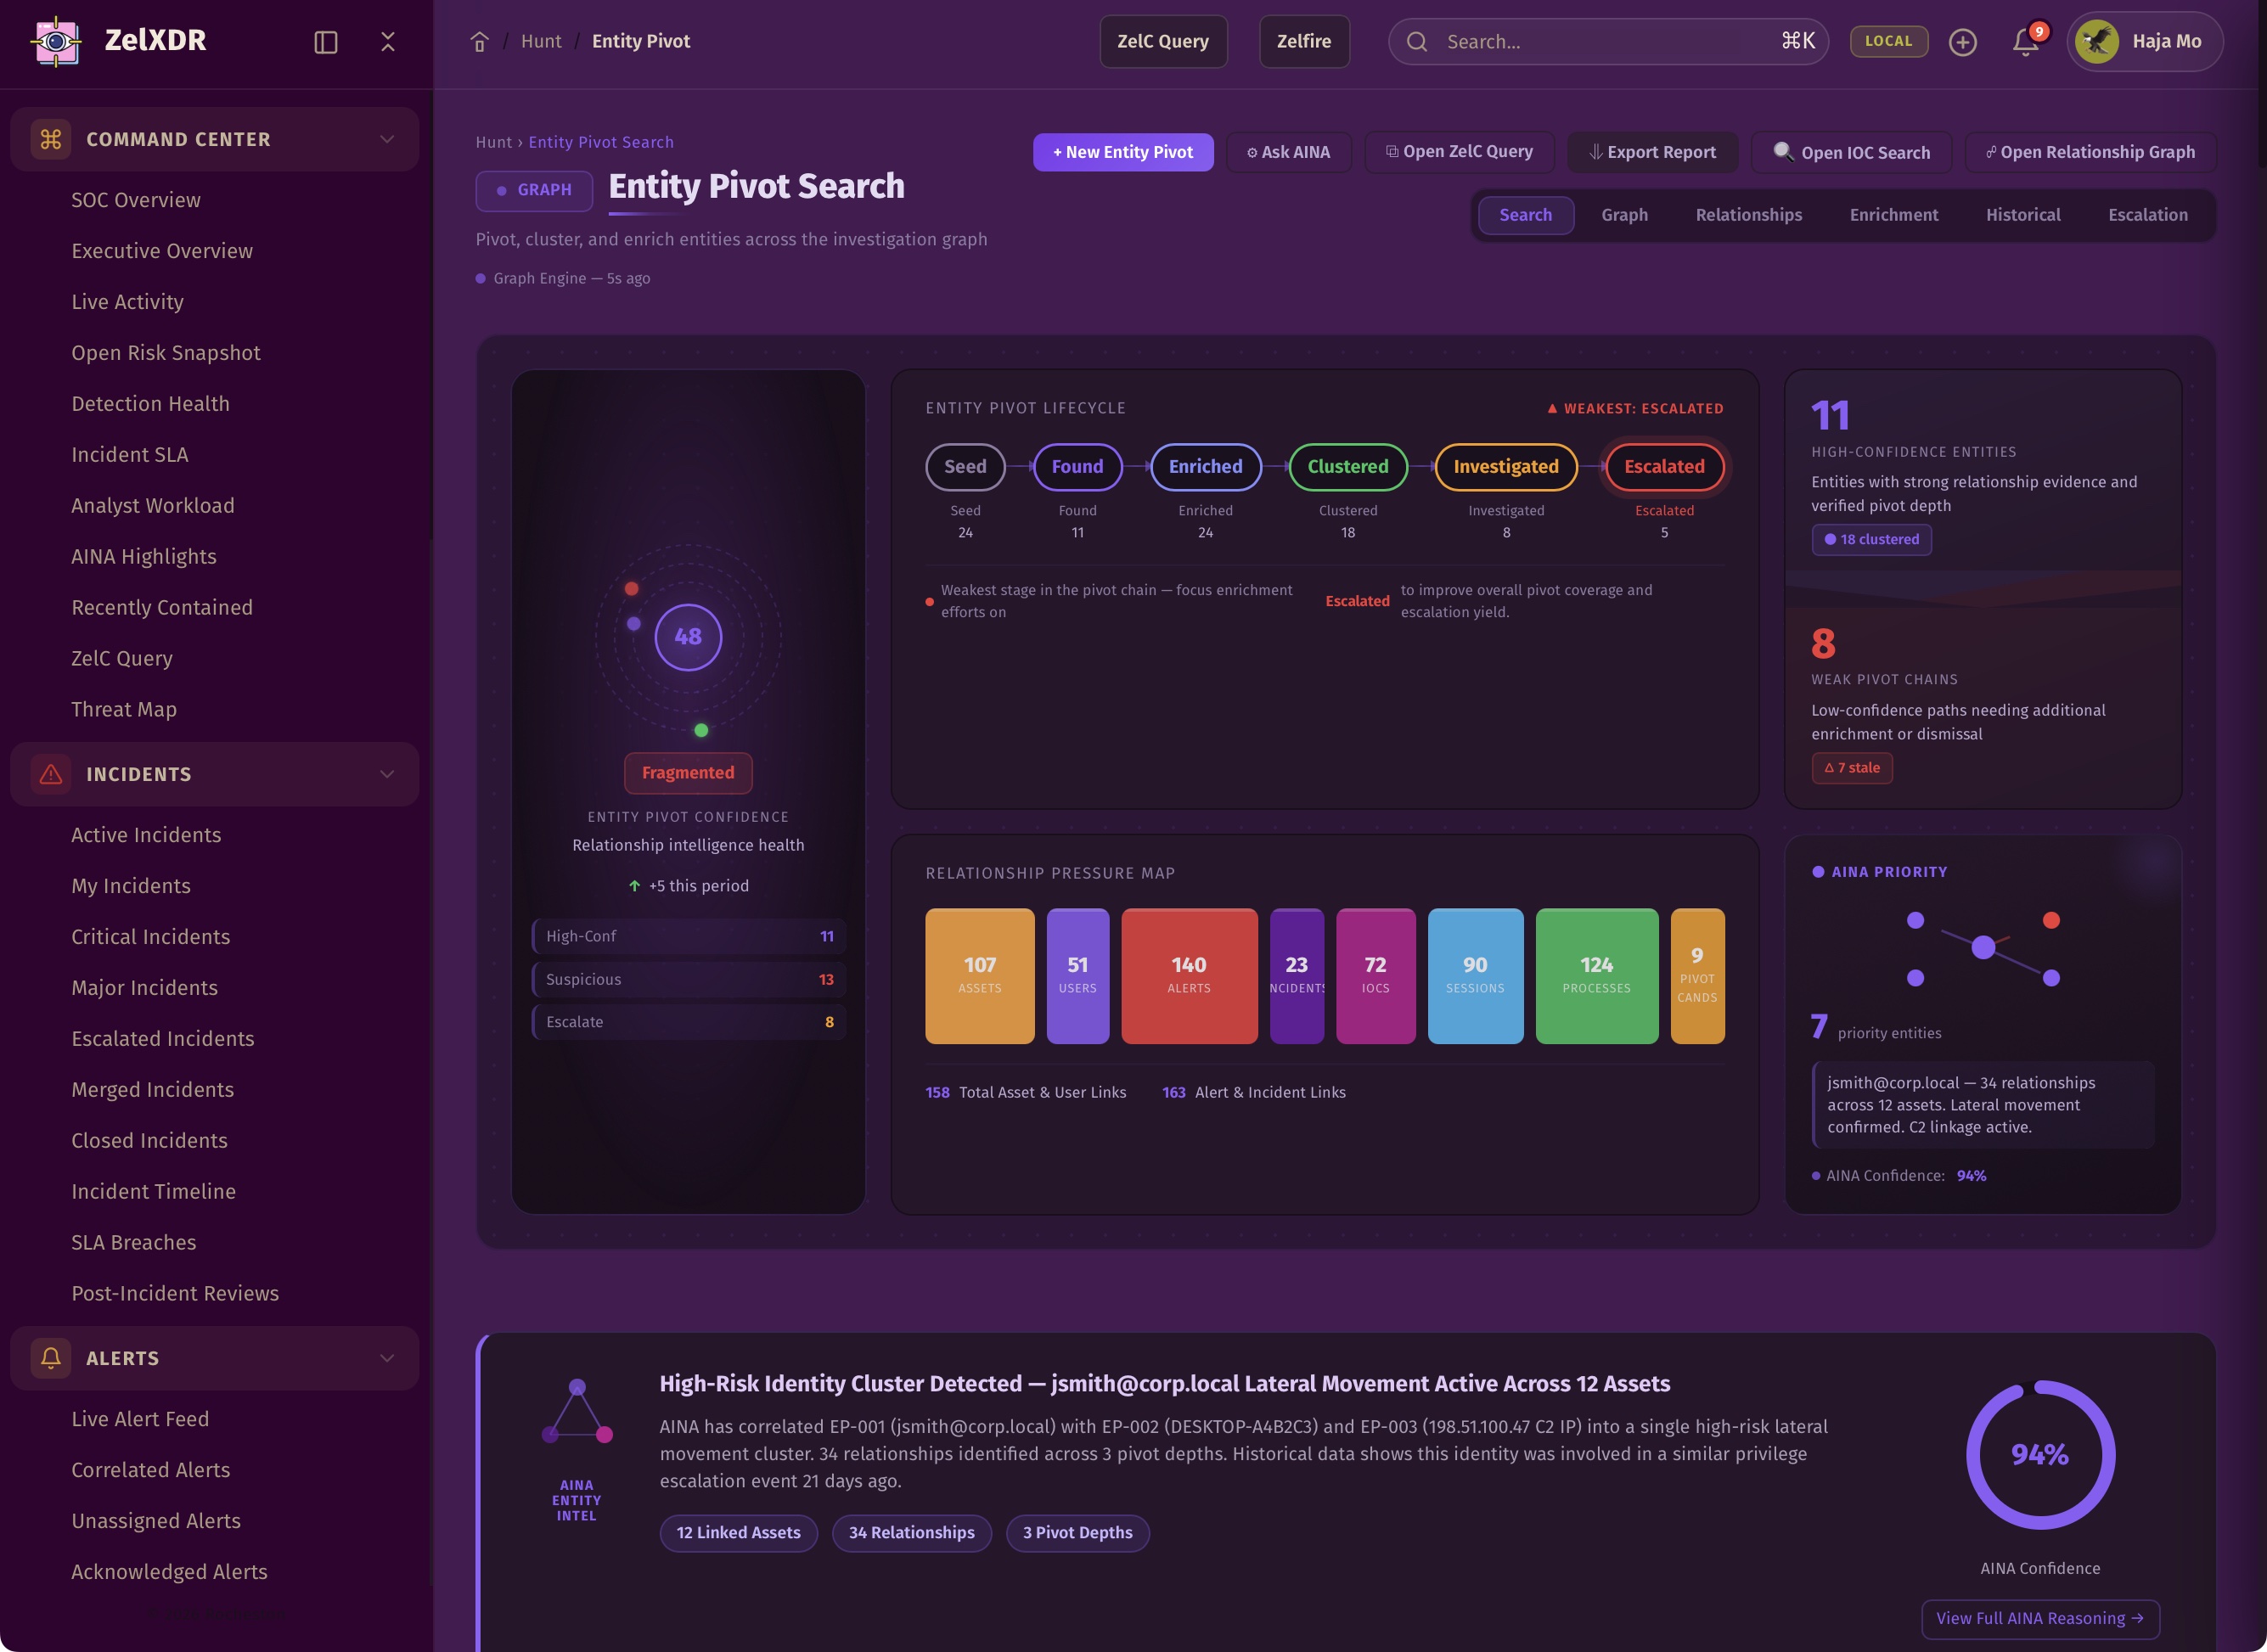
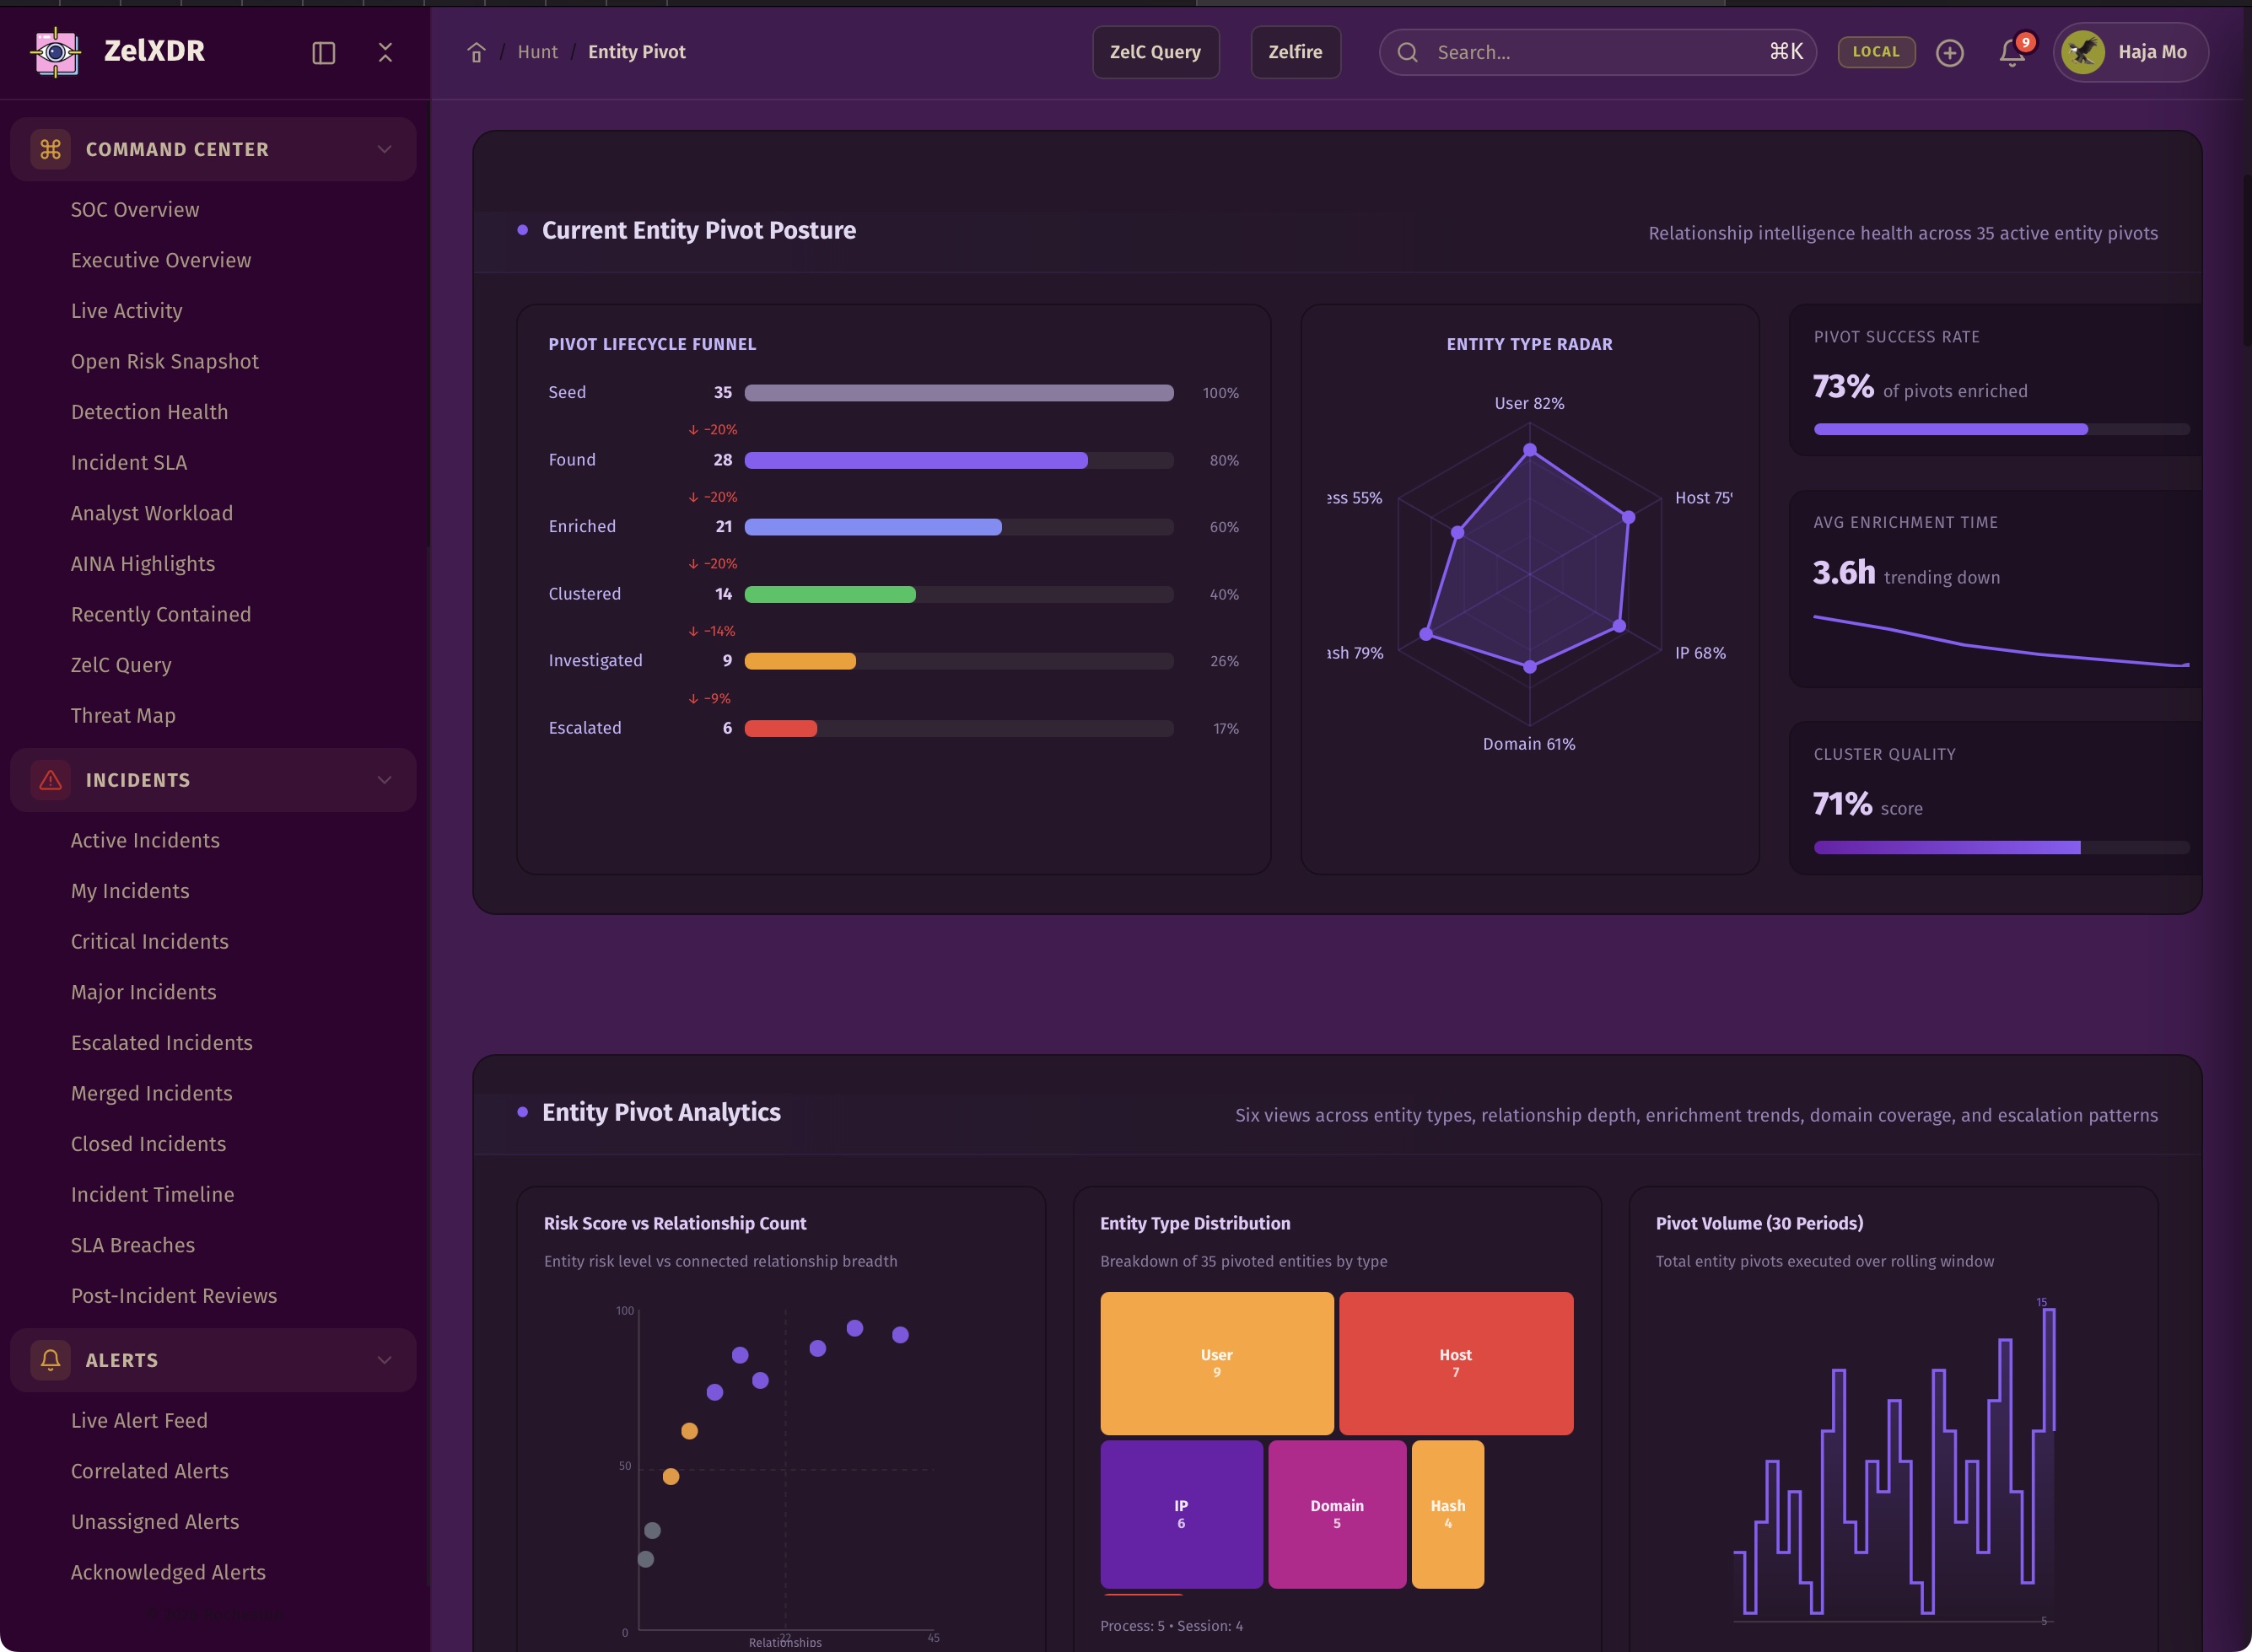
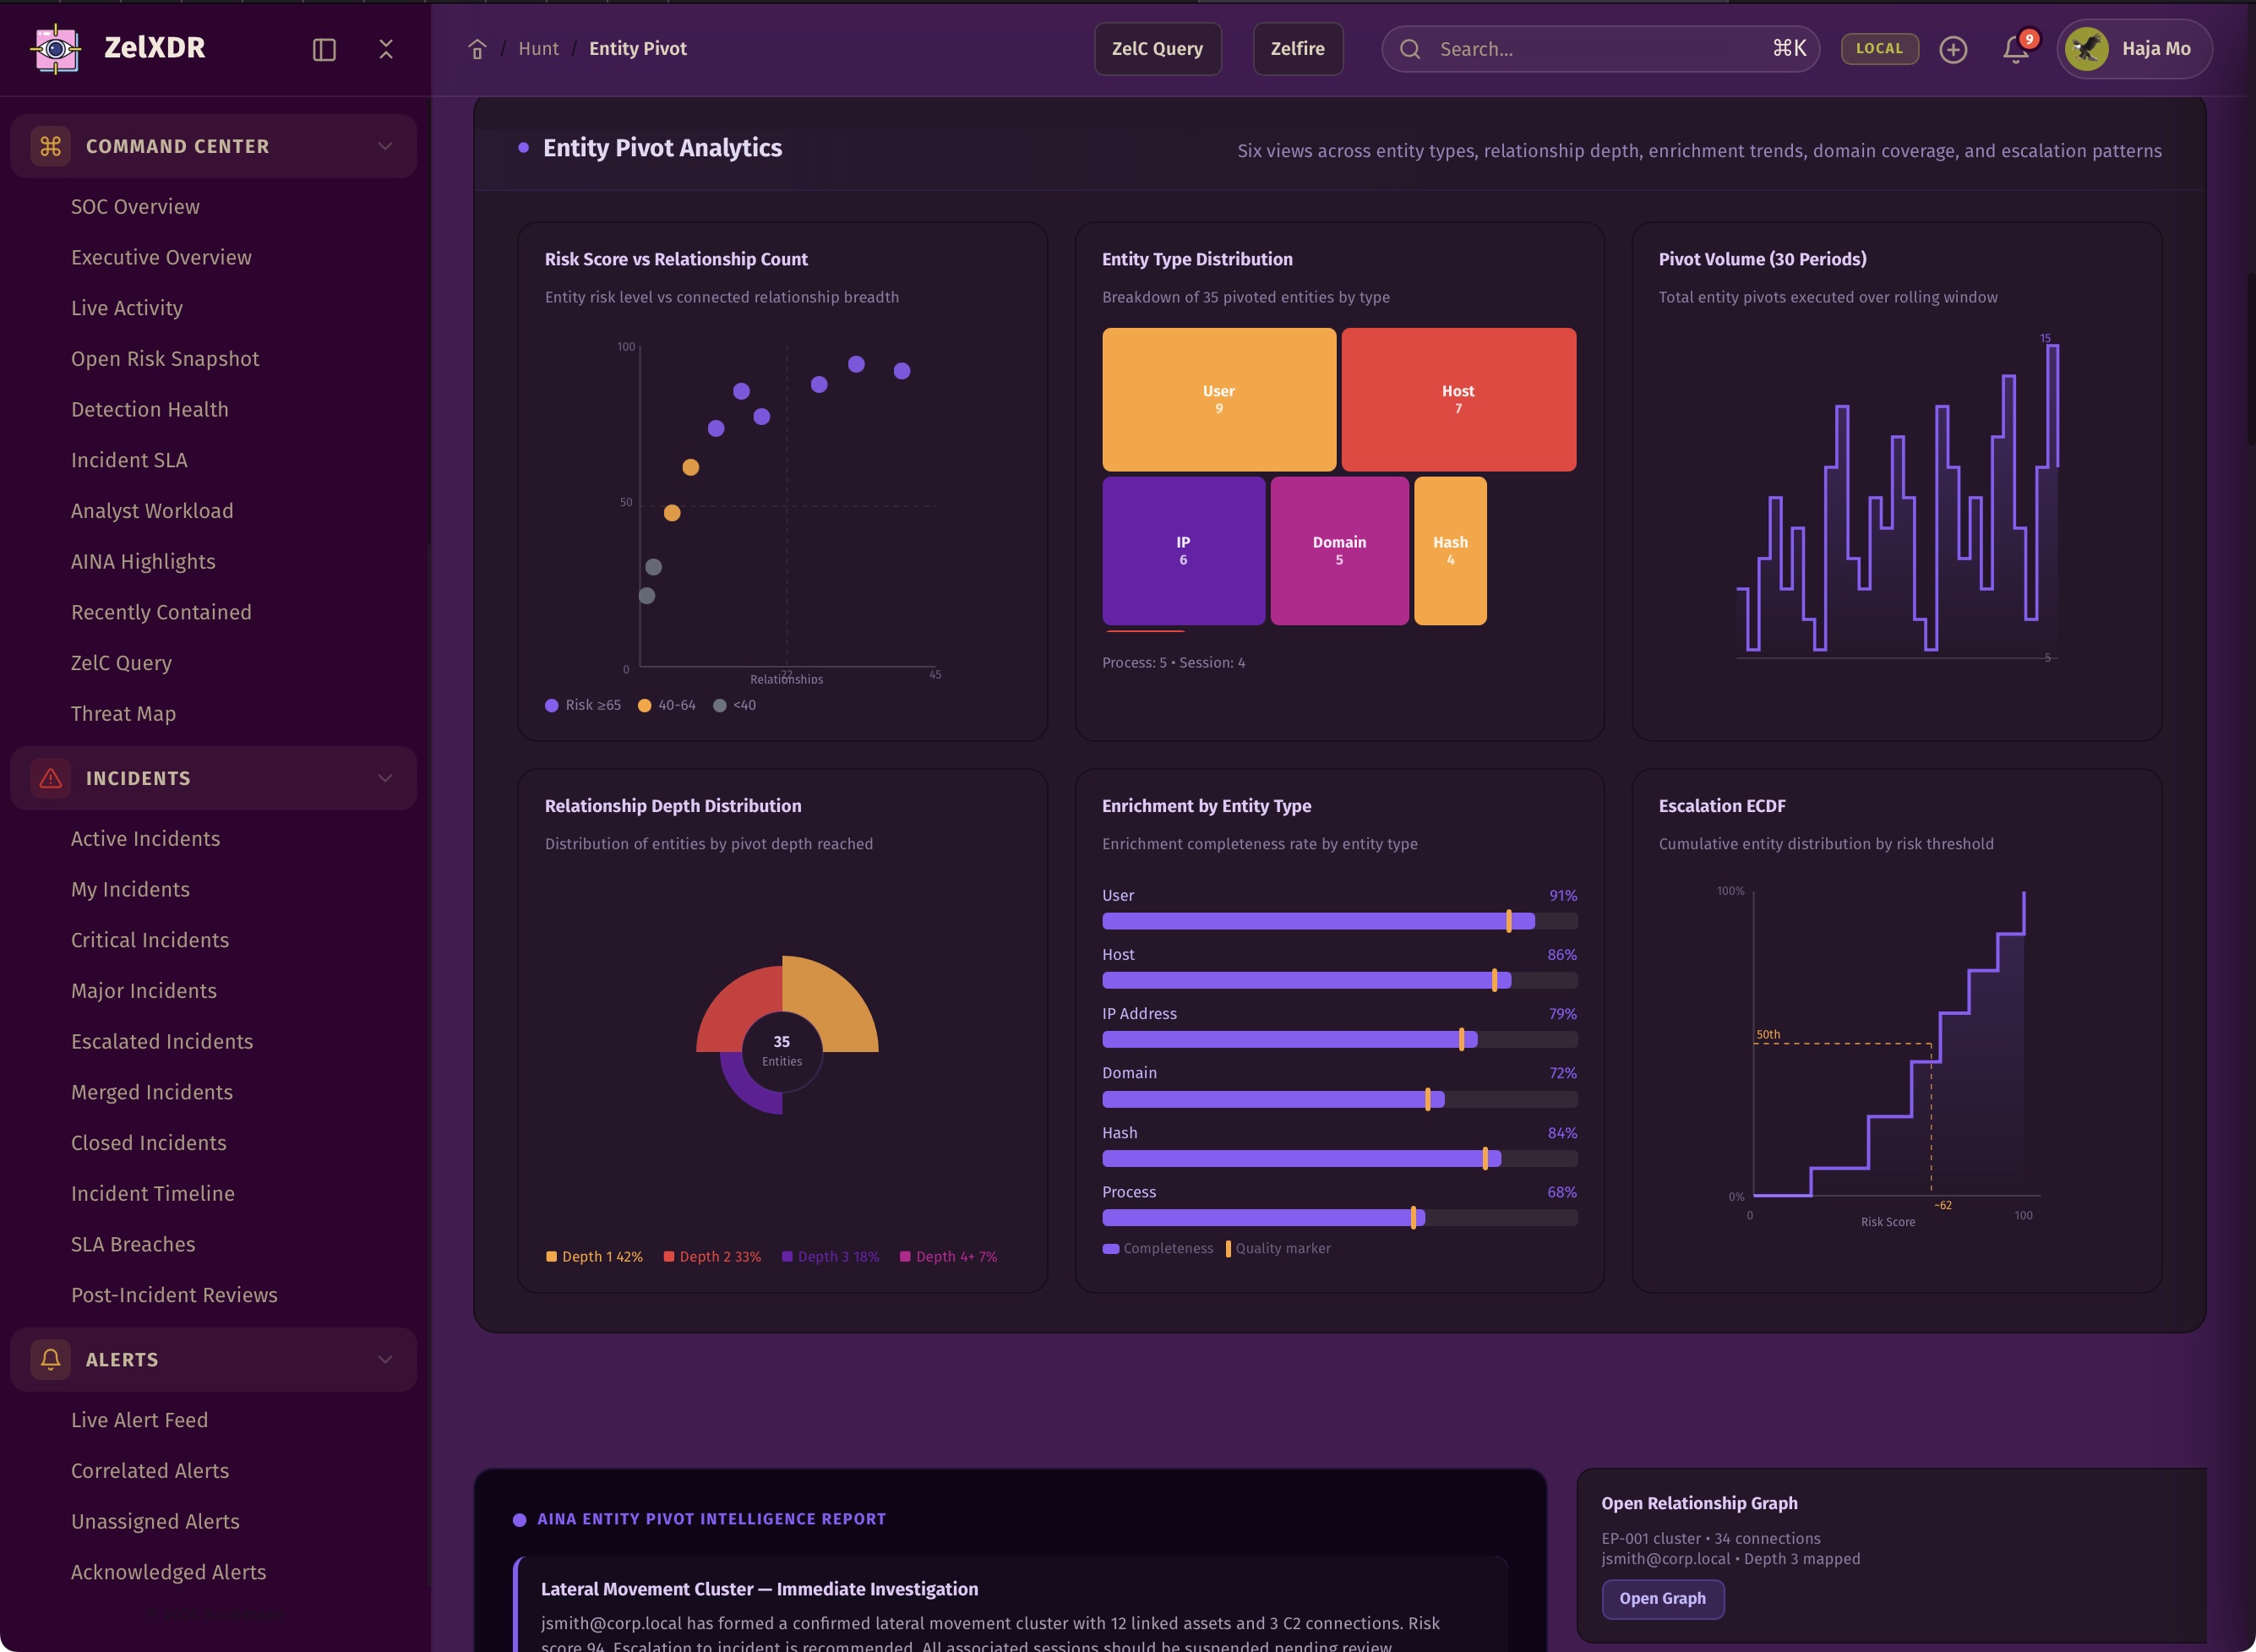
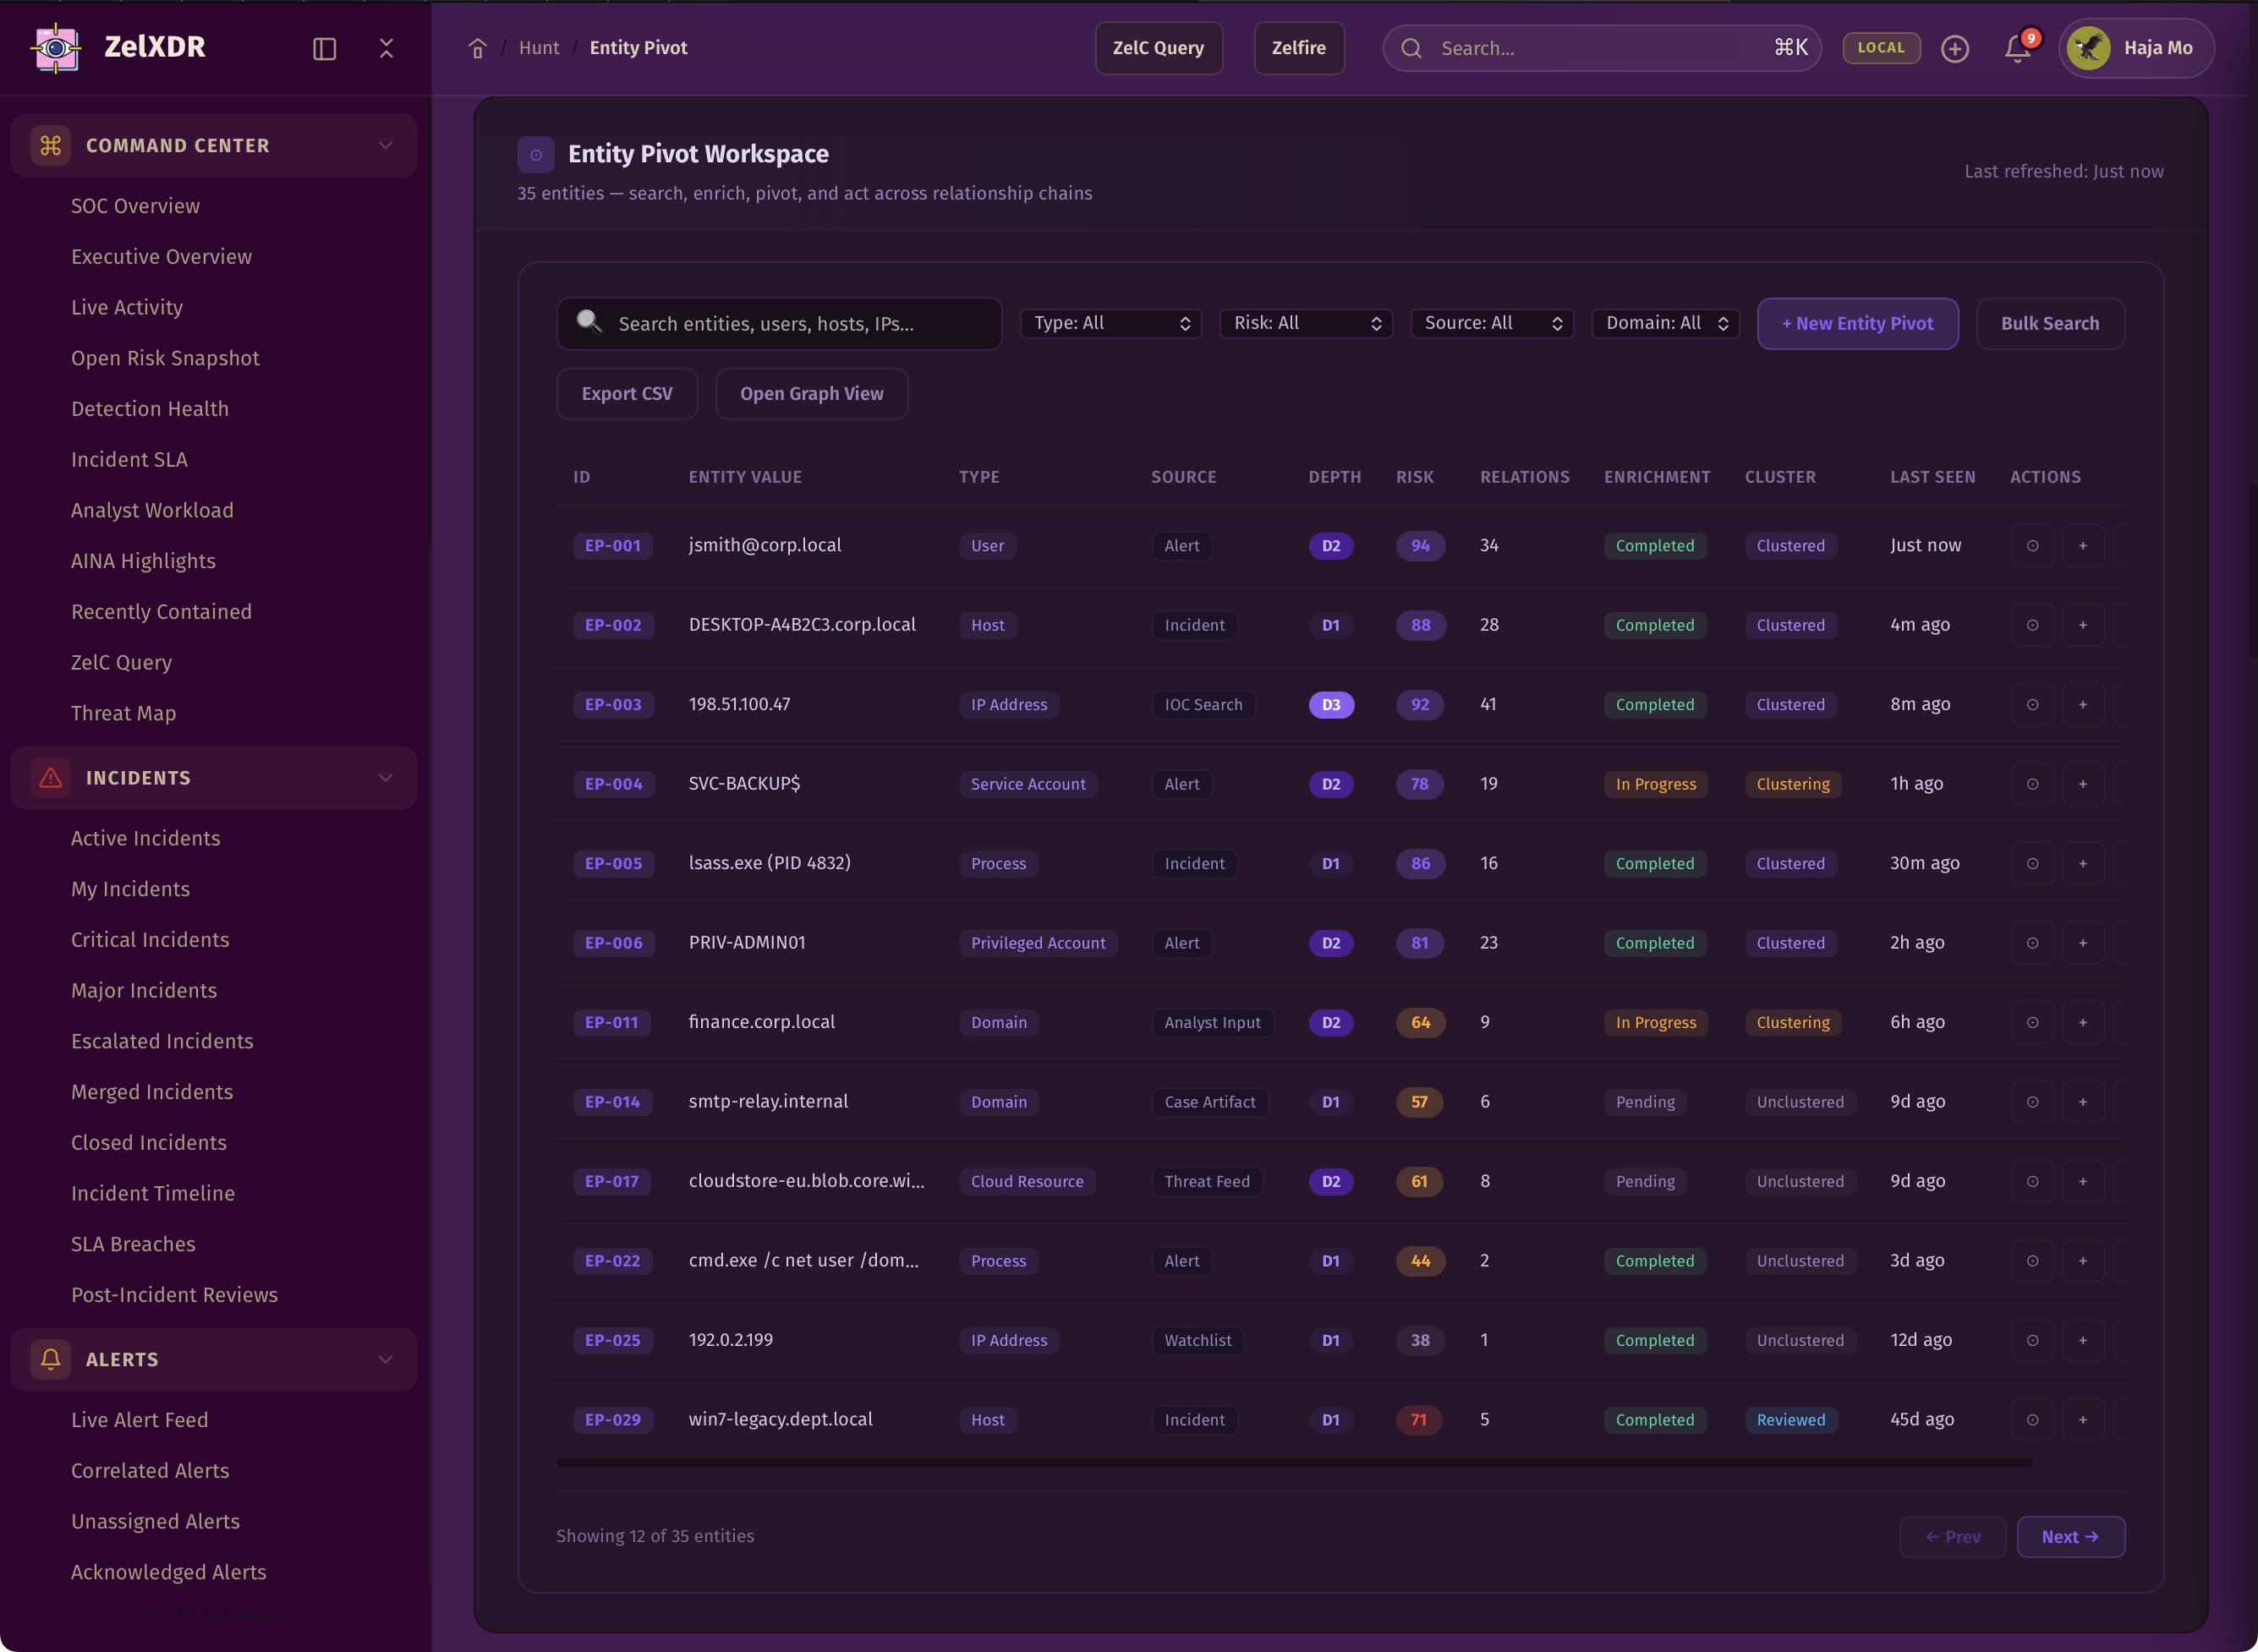
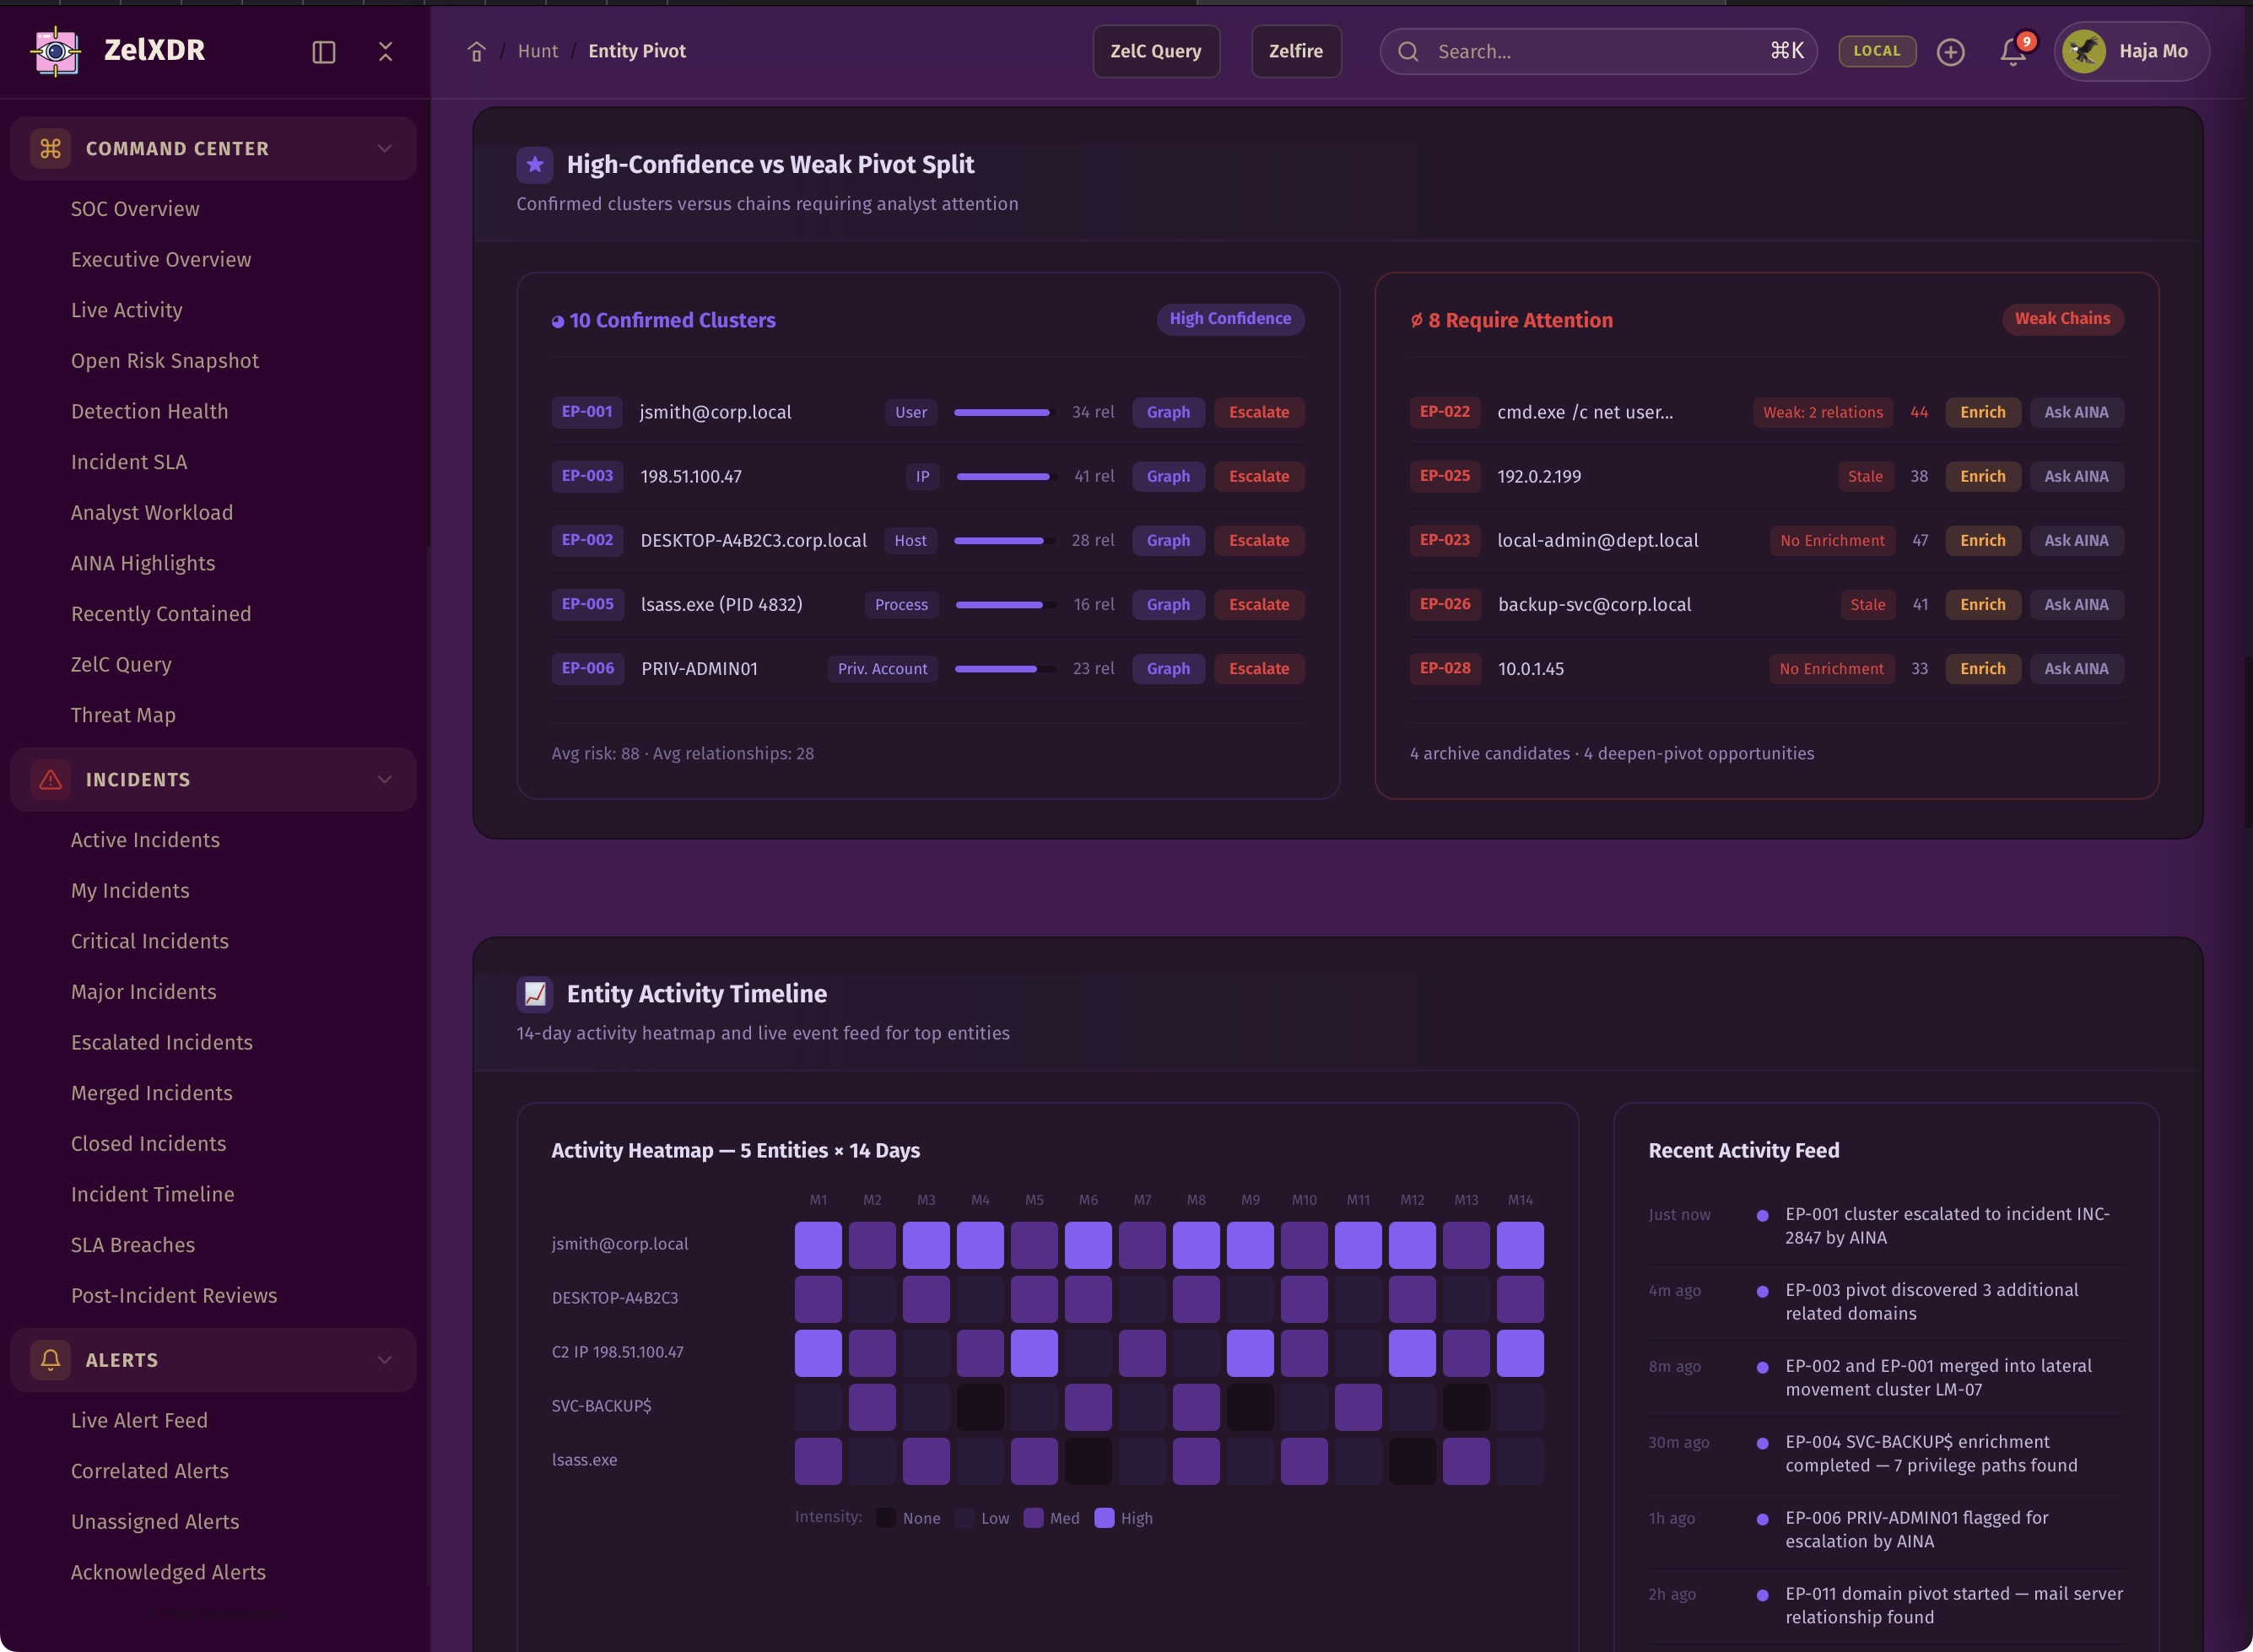
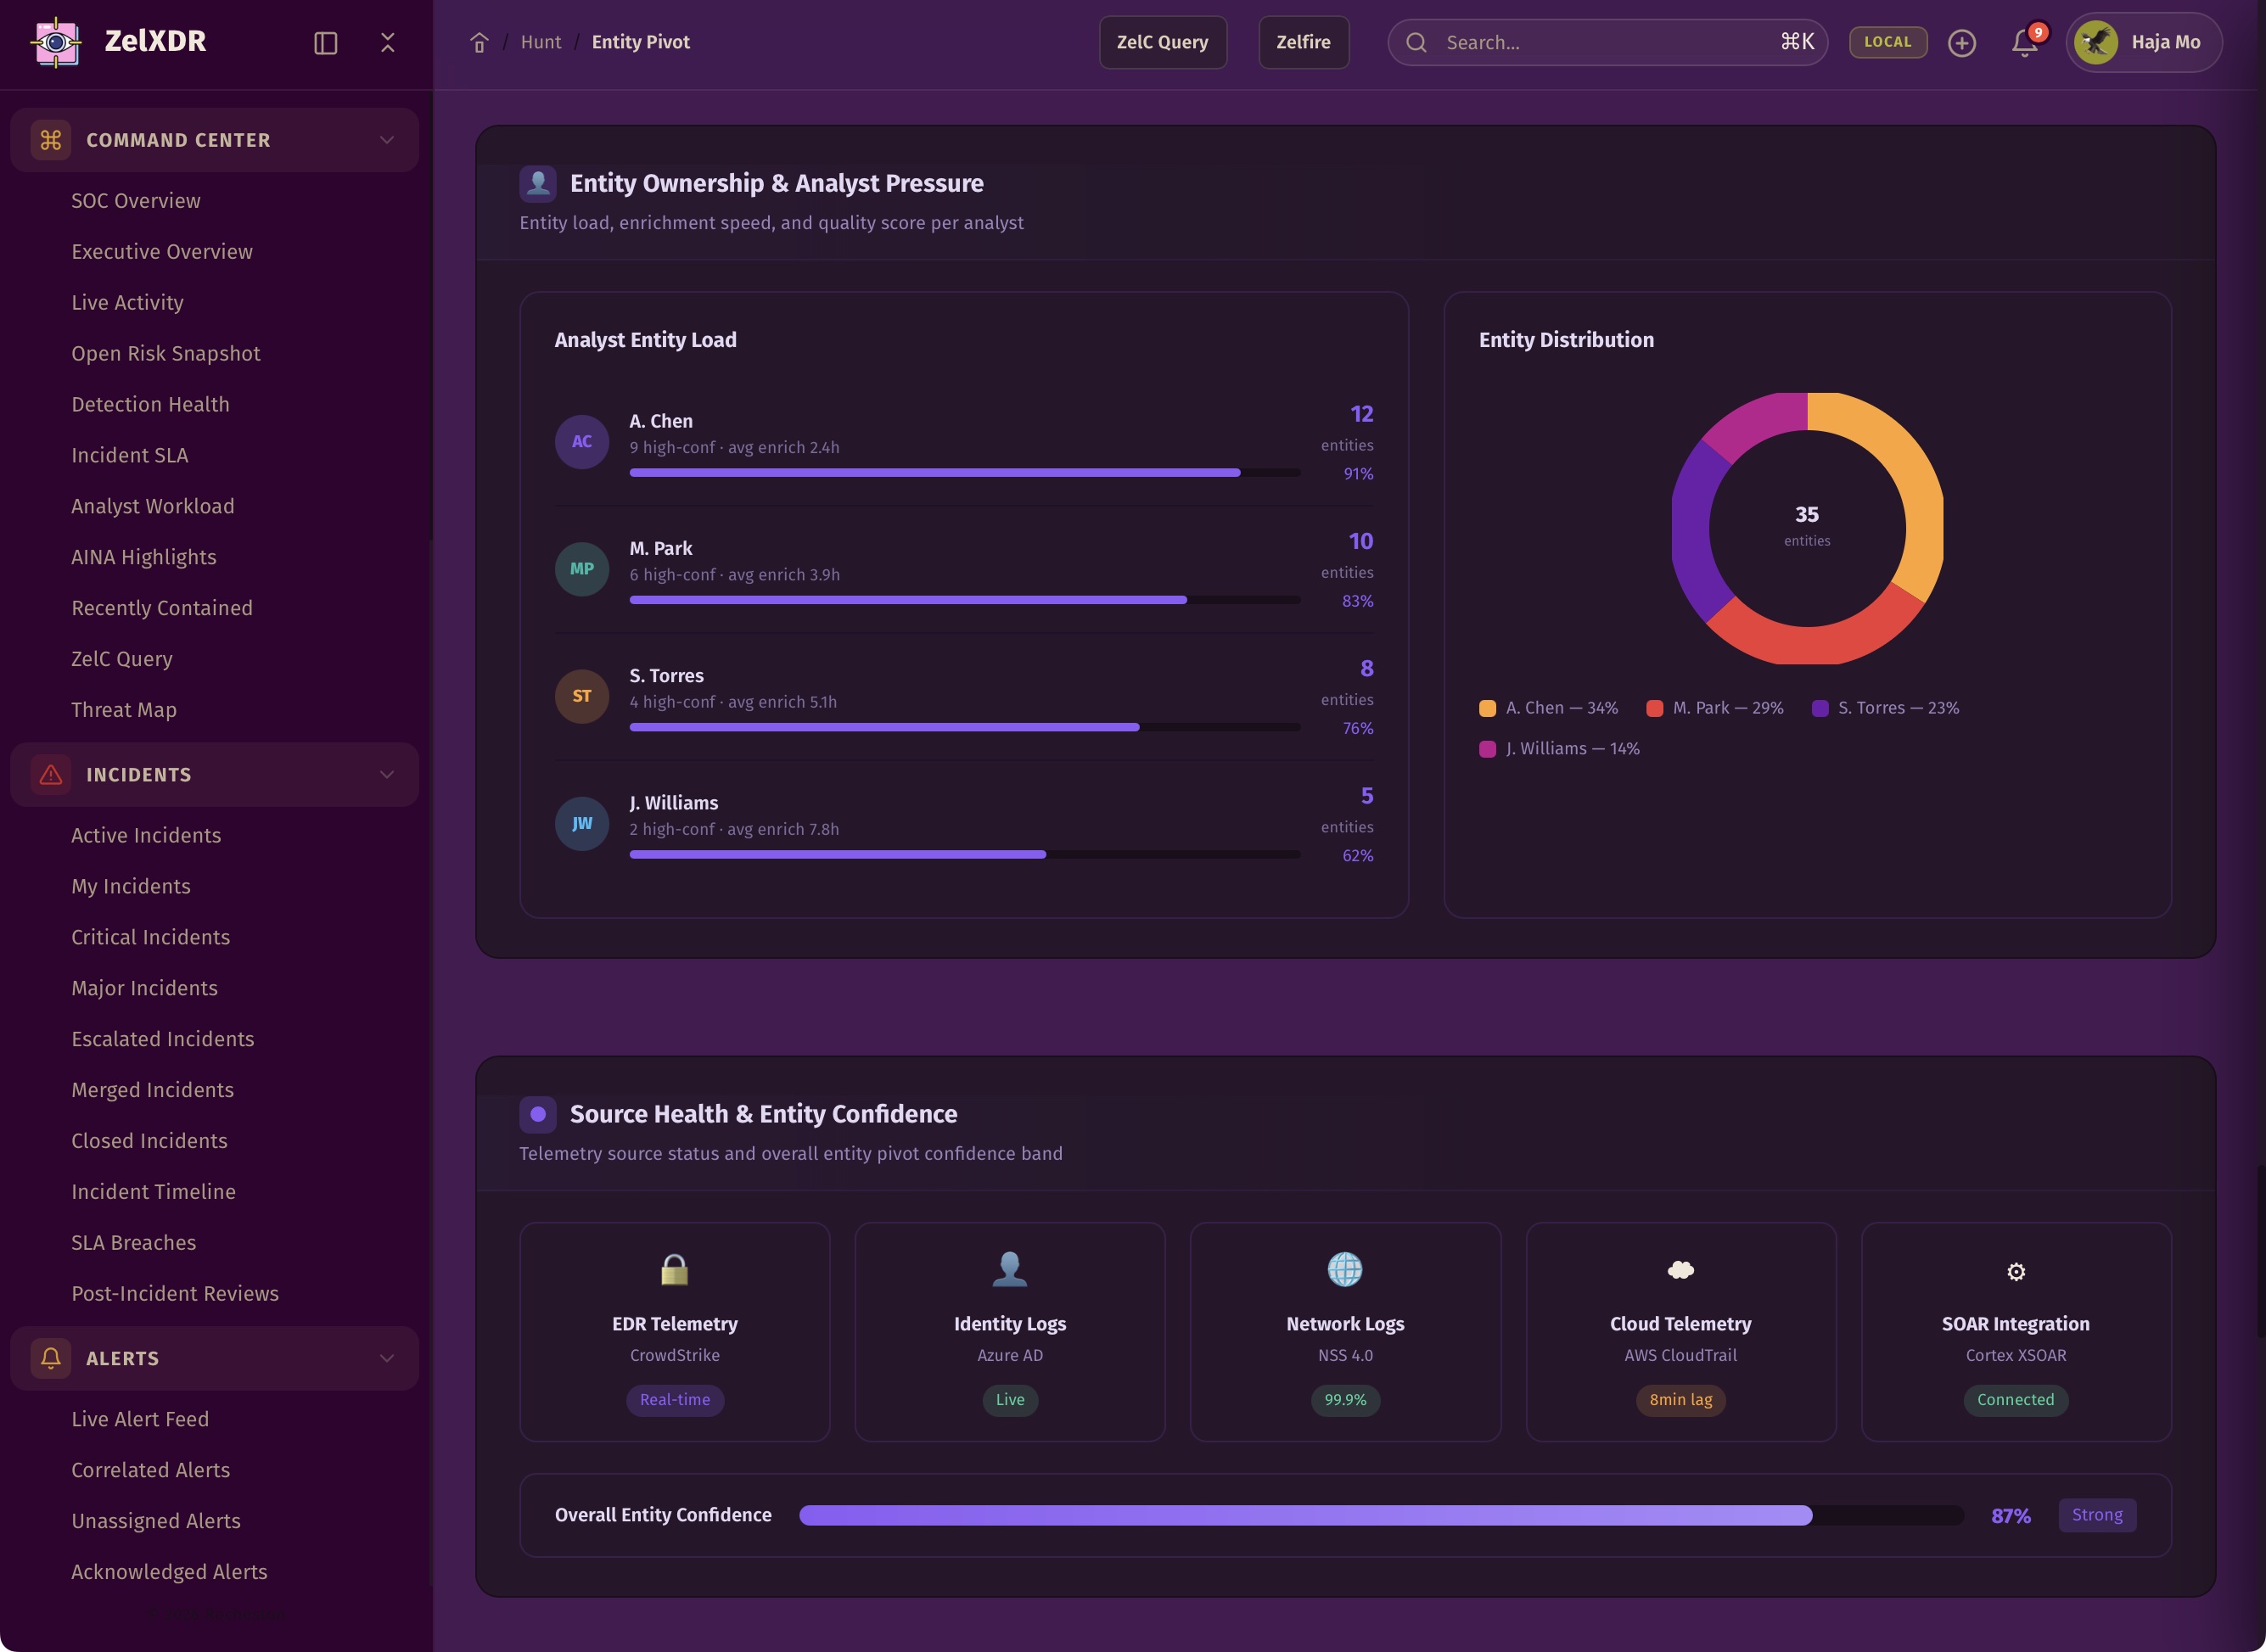
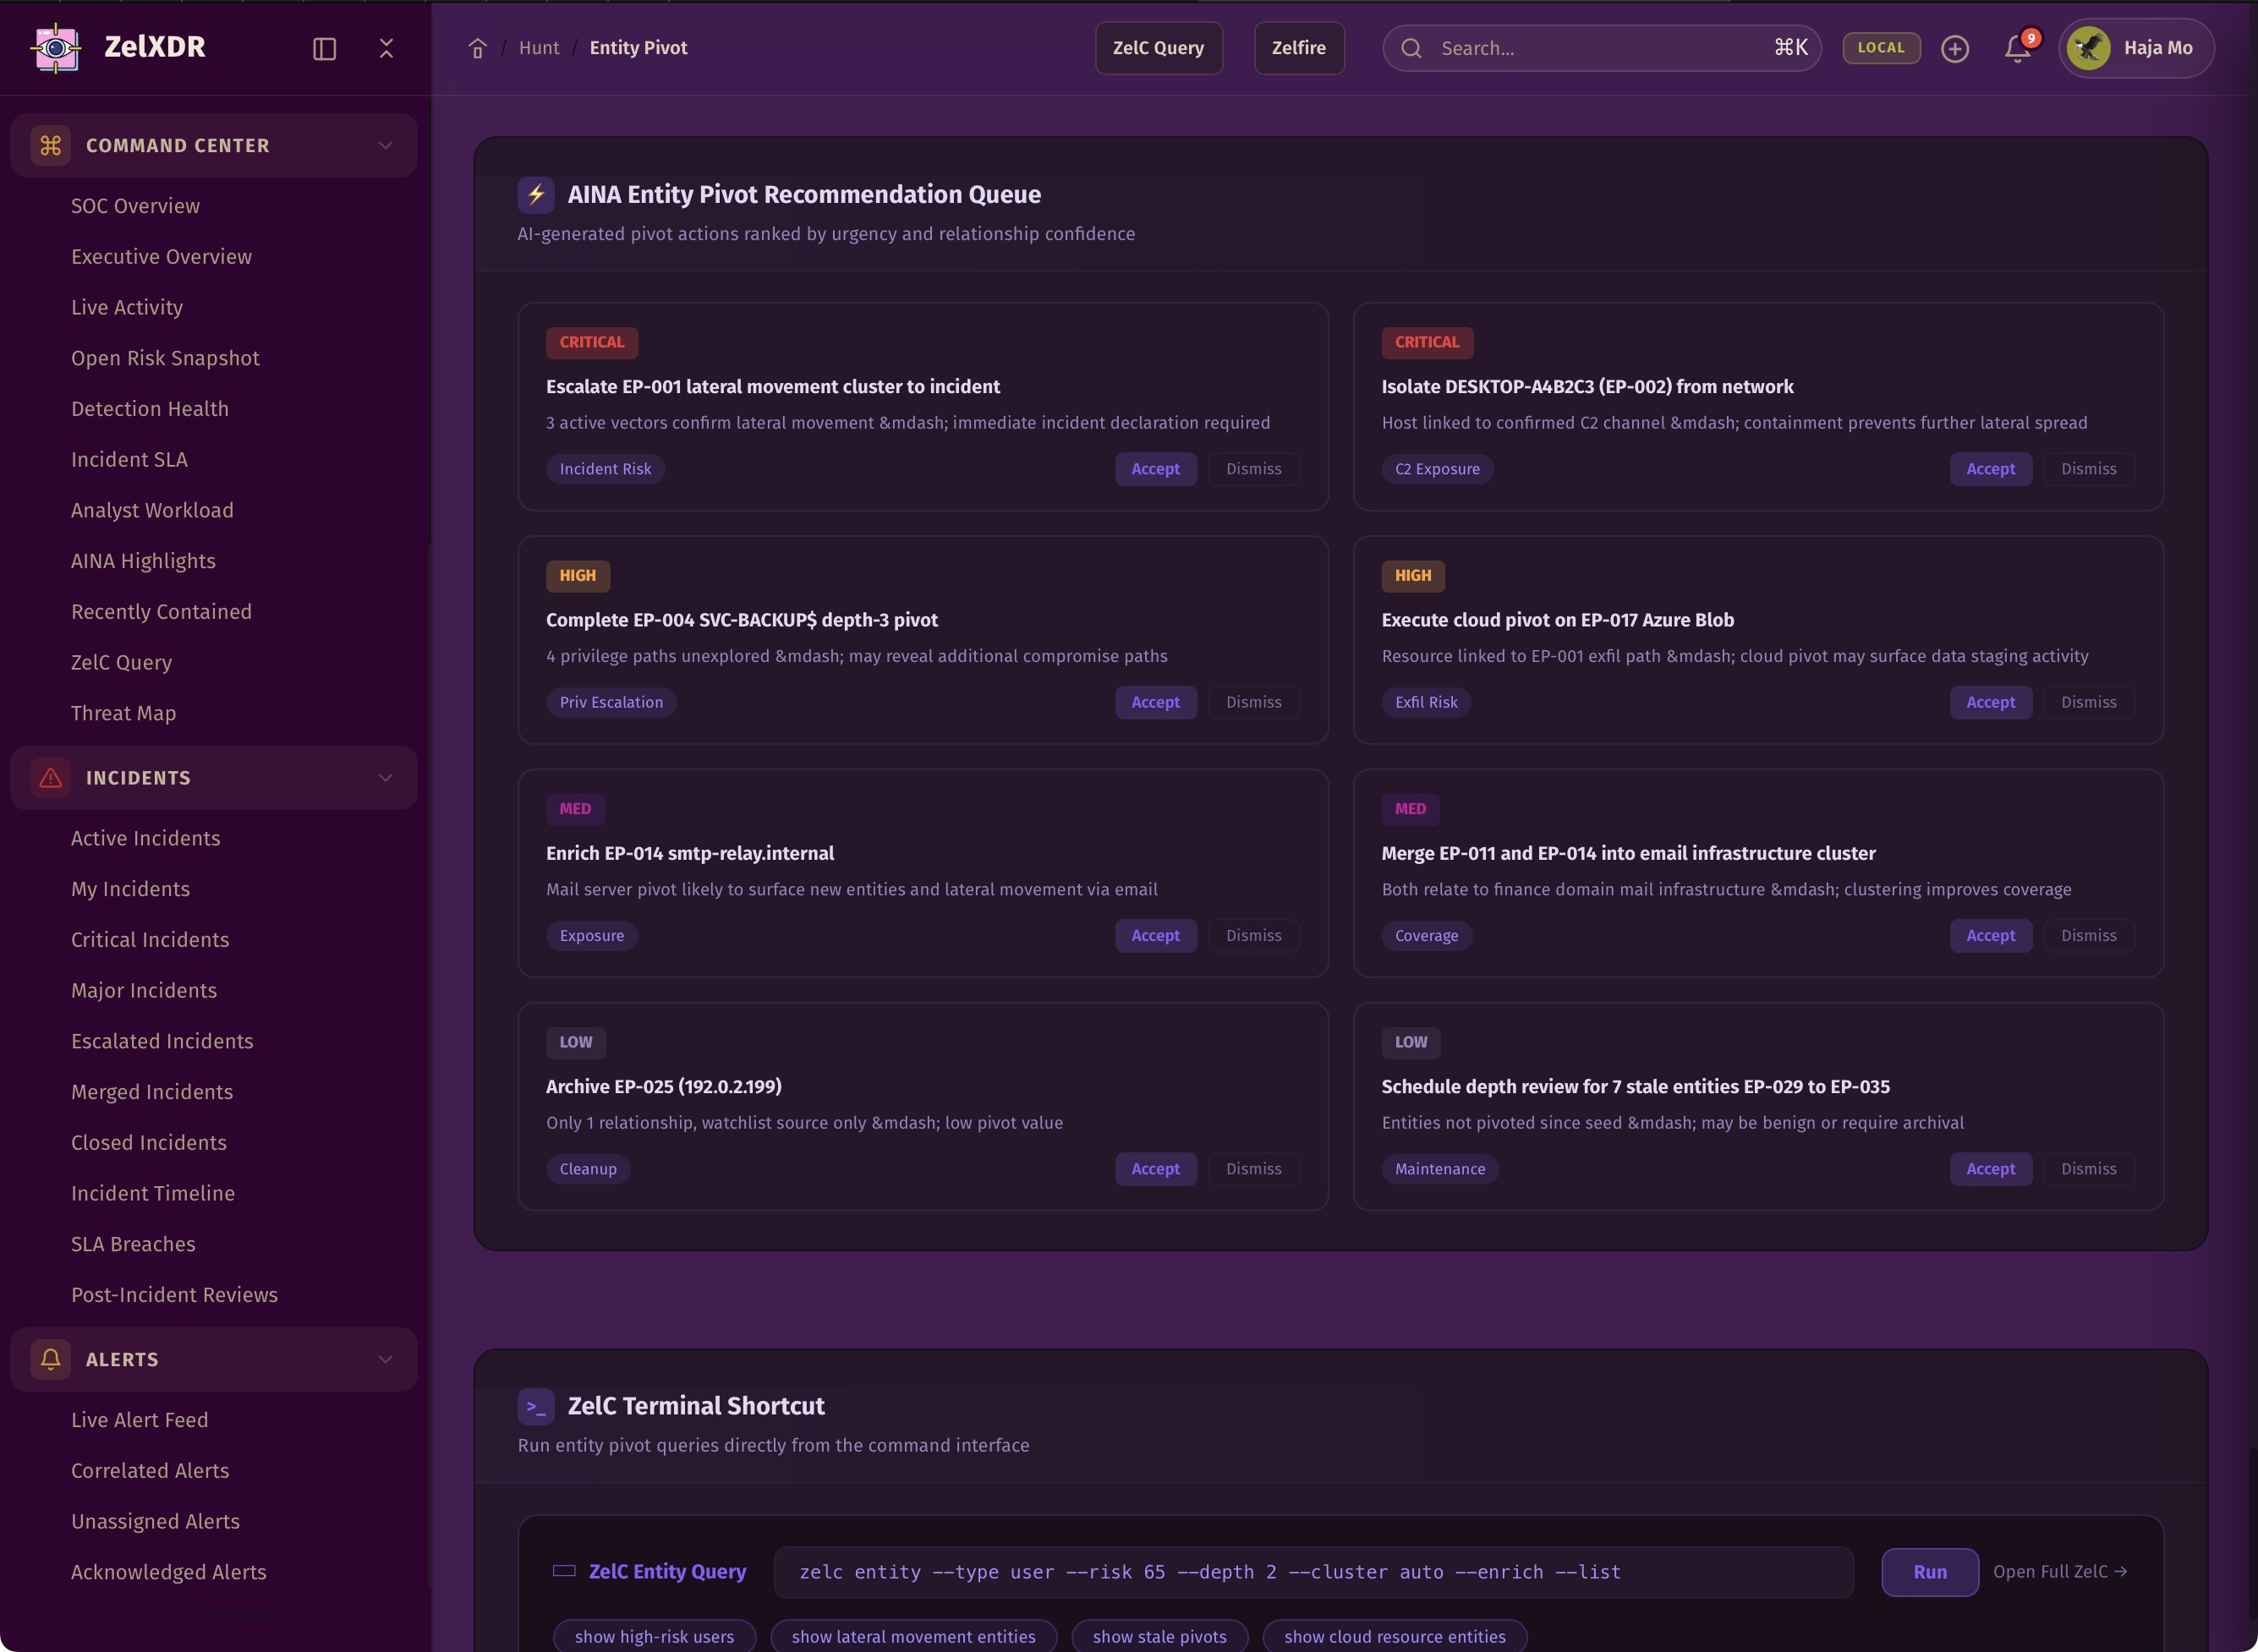
ZelXDR allows investigators to pivot across users, hosts, service accounts, cloud assets, IPs, processes, sessions, and related objects to reveal suspicious relationships and hidden clusters.
Entities tell the story that isolated alerts cannot.
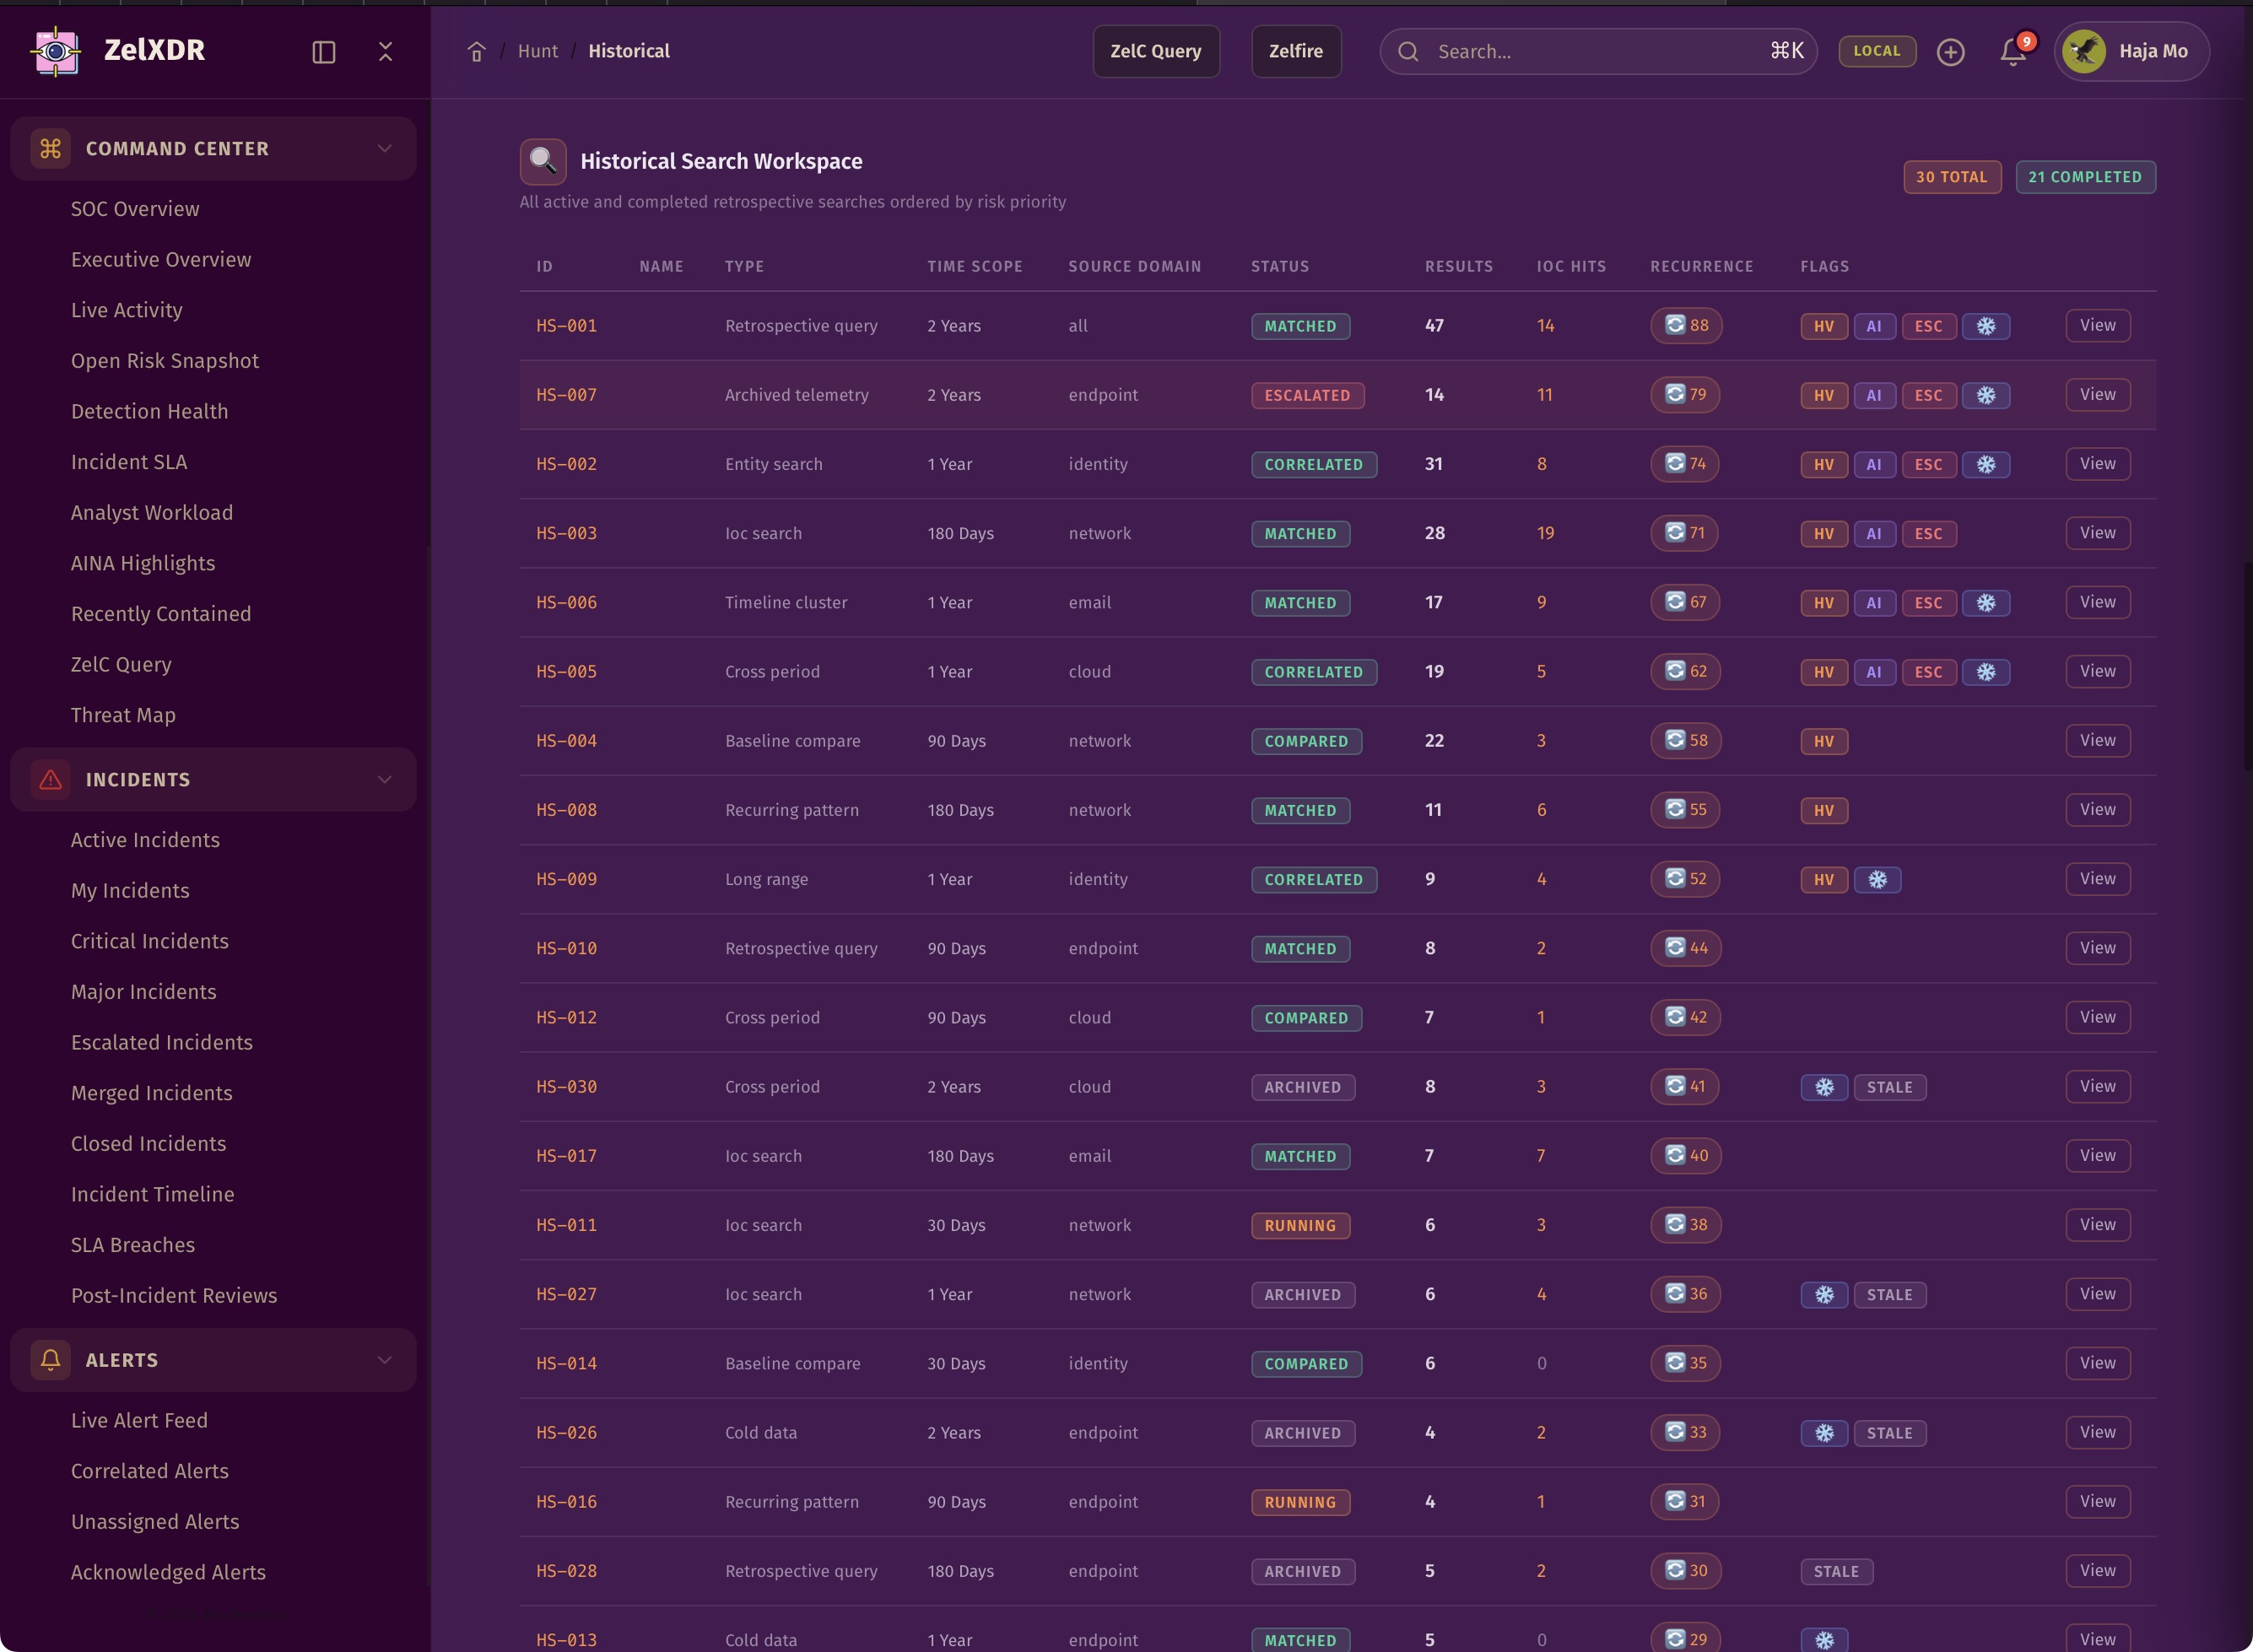
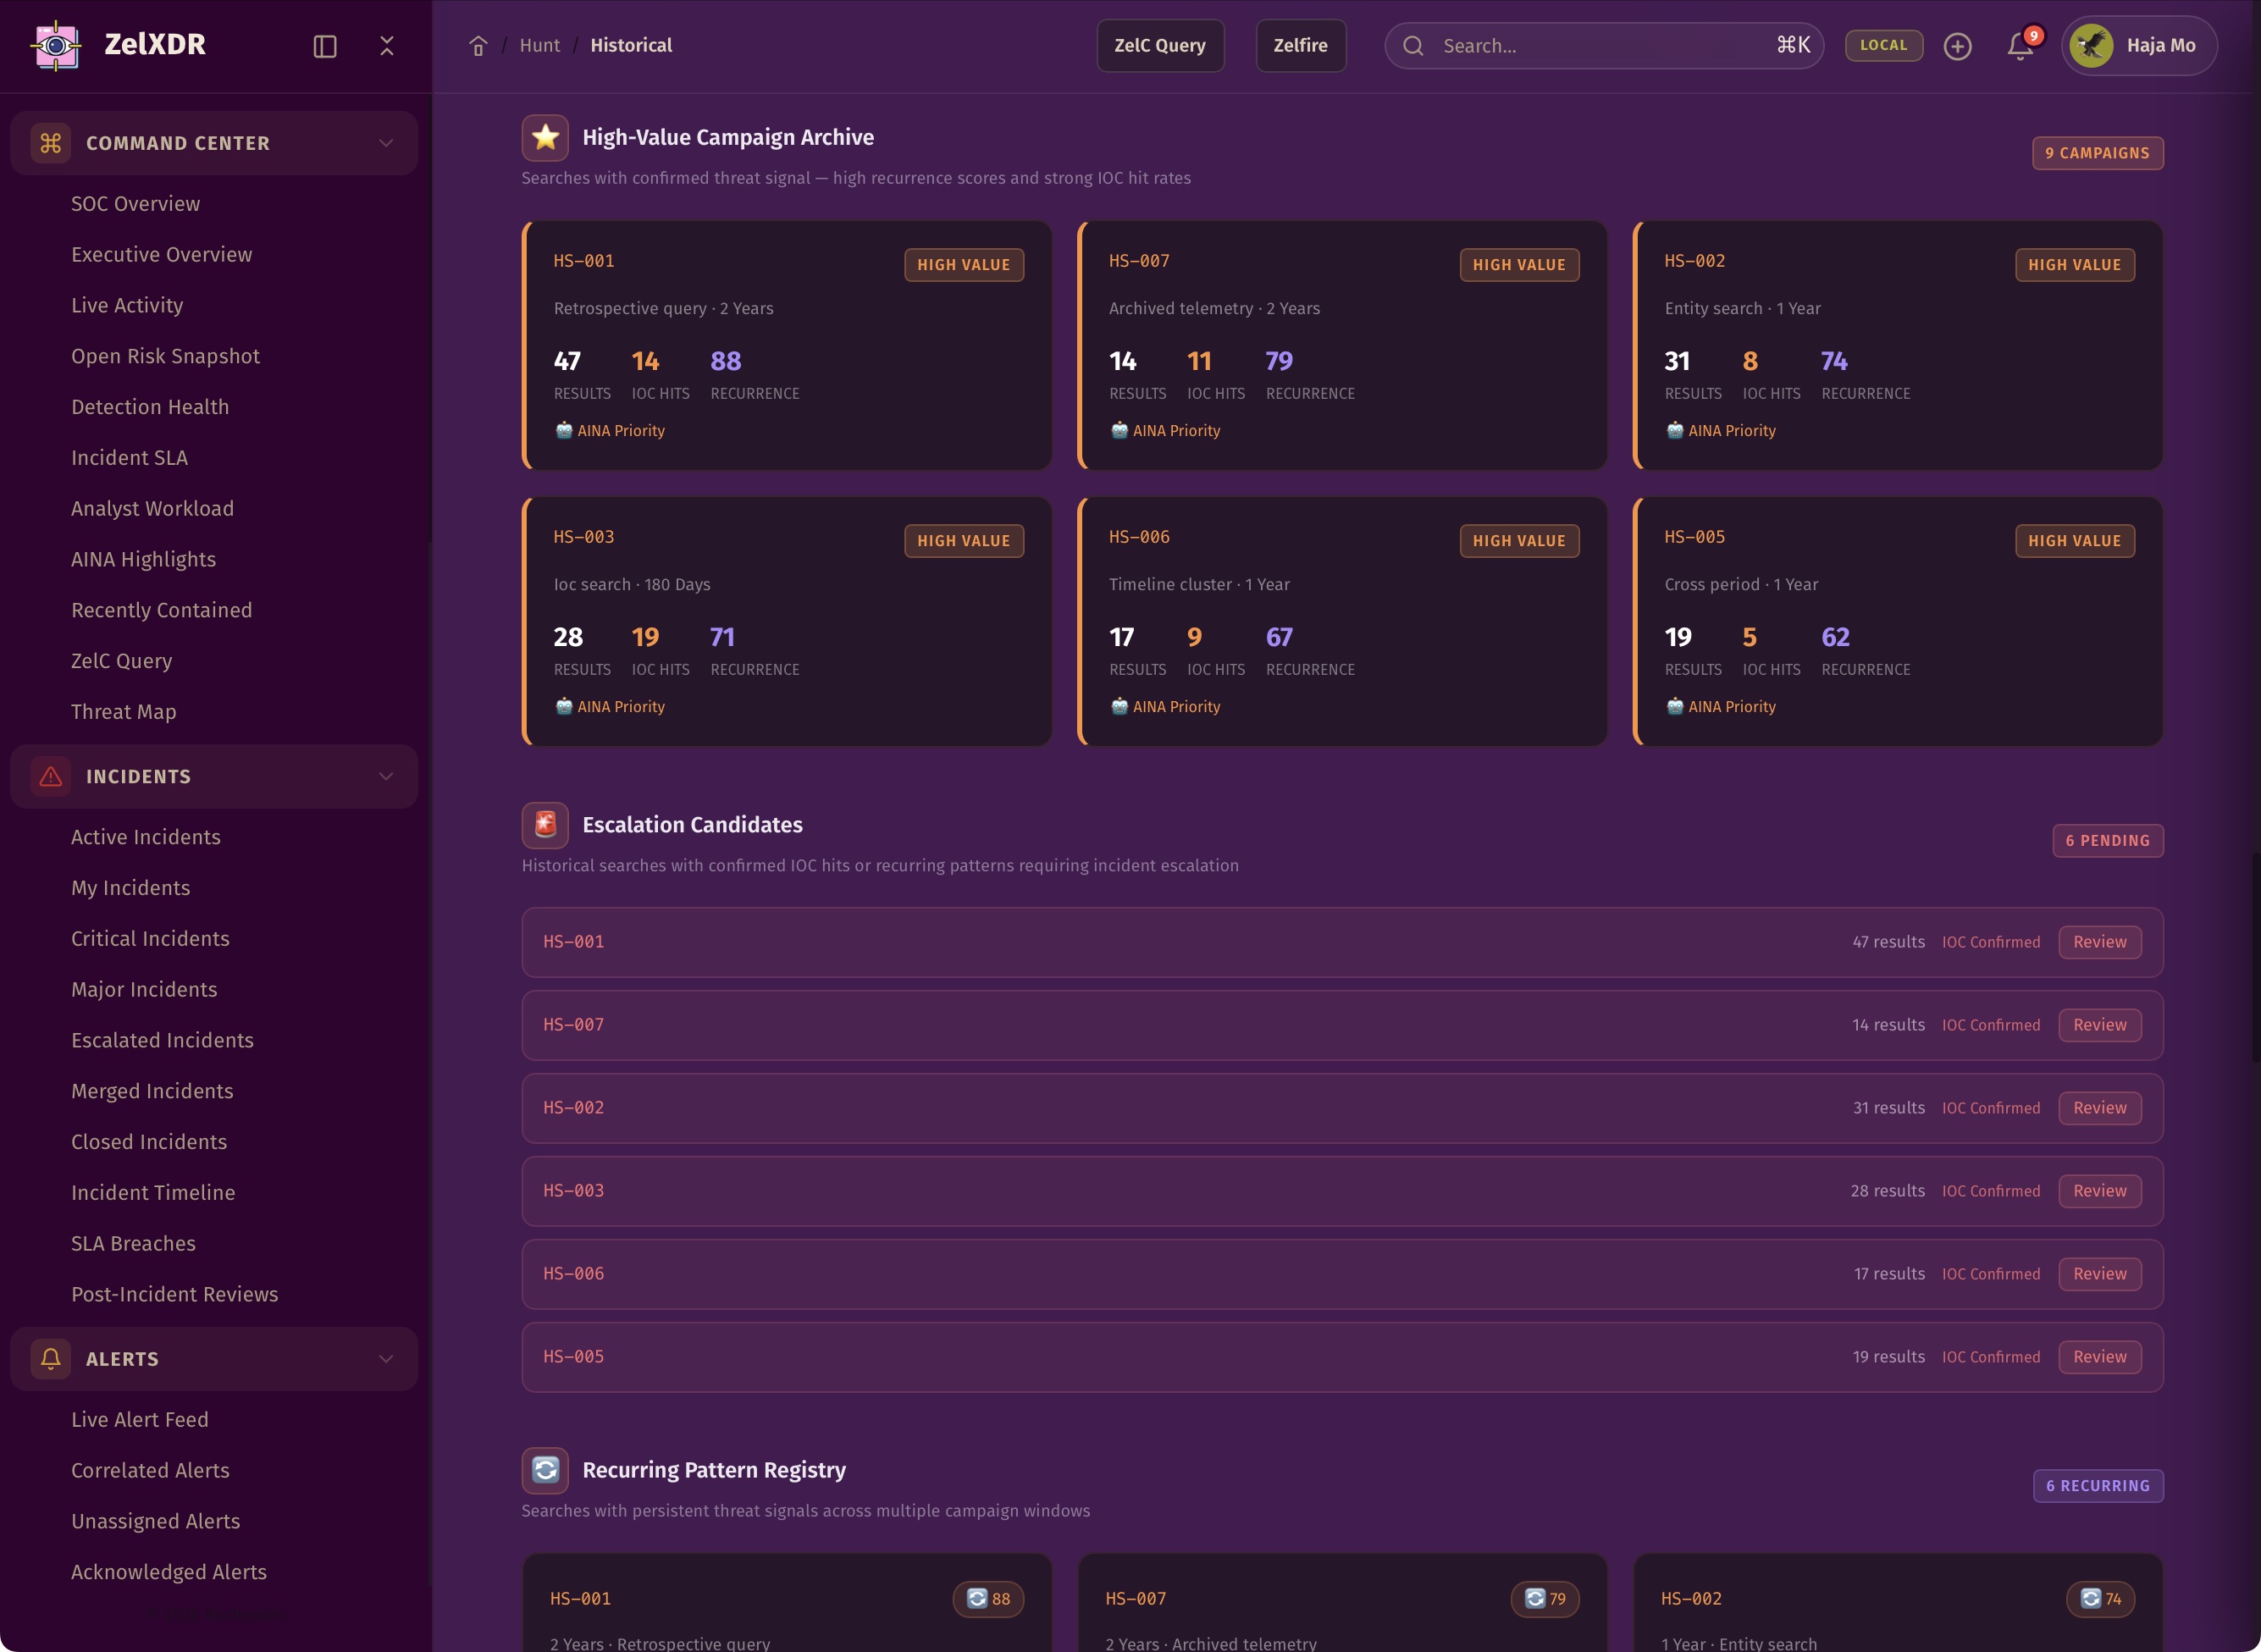
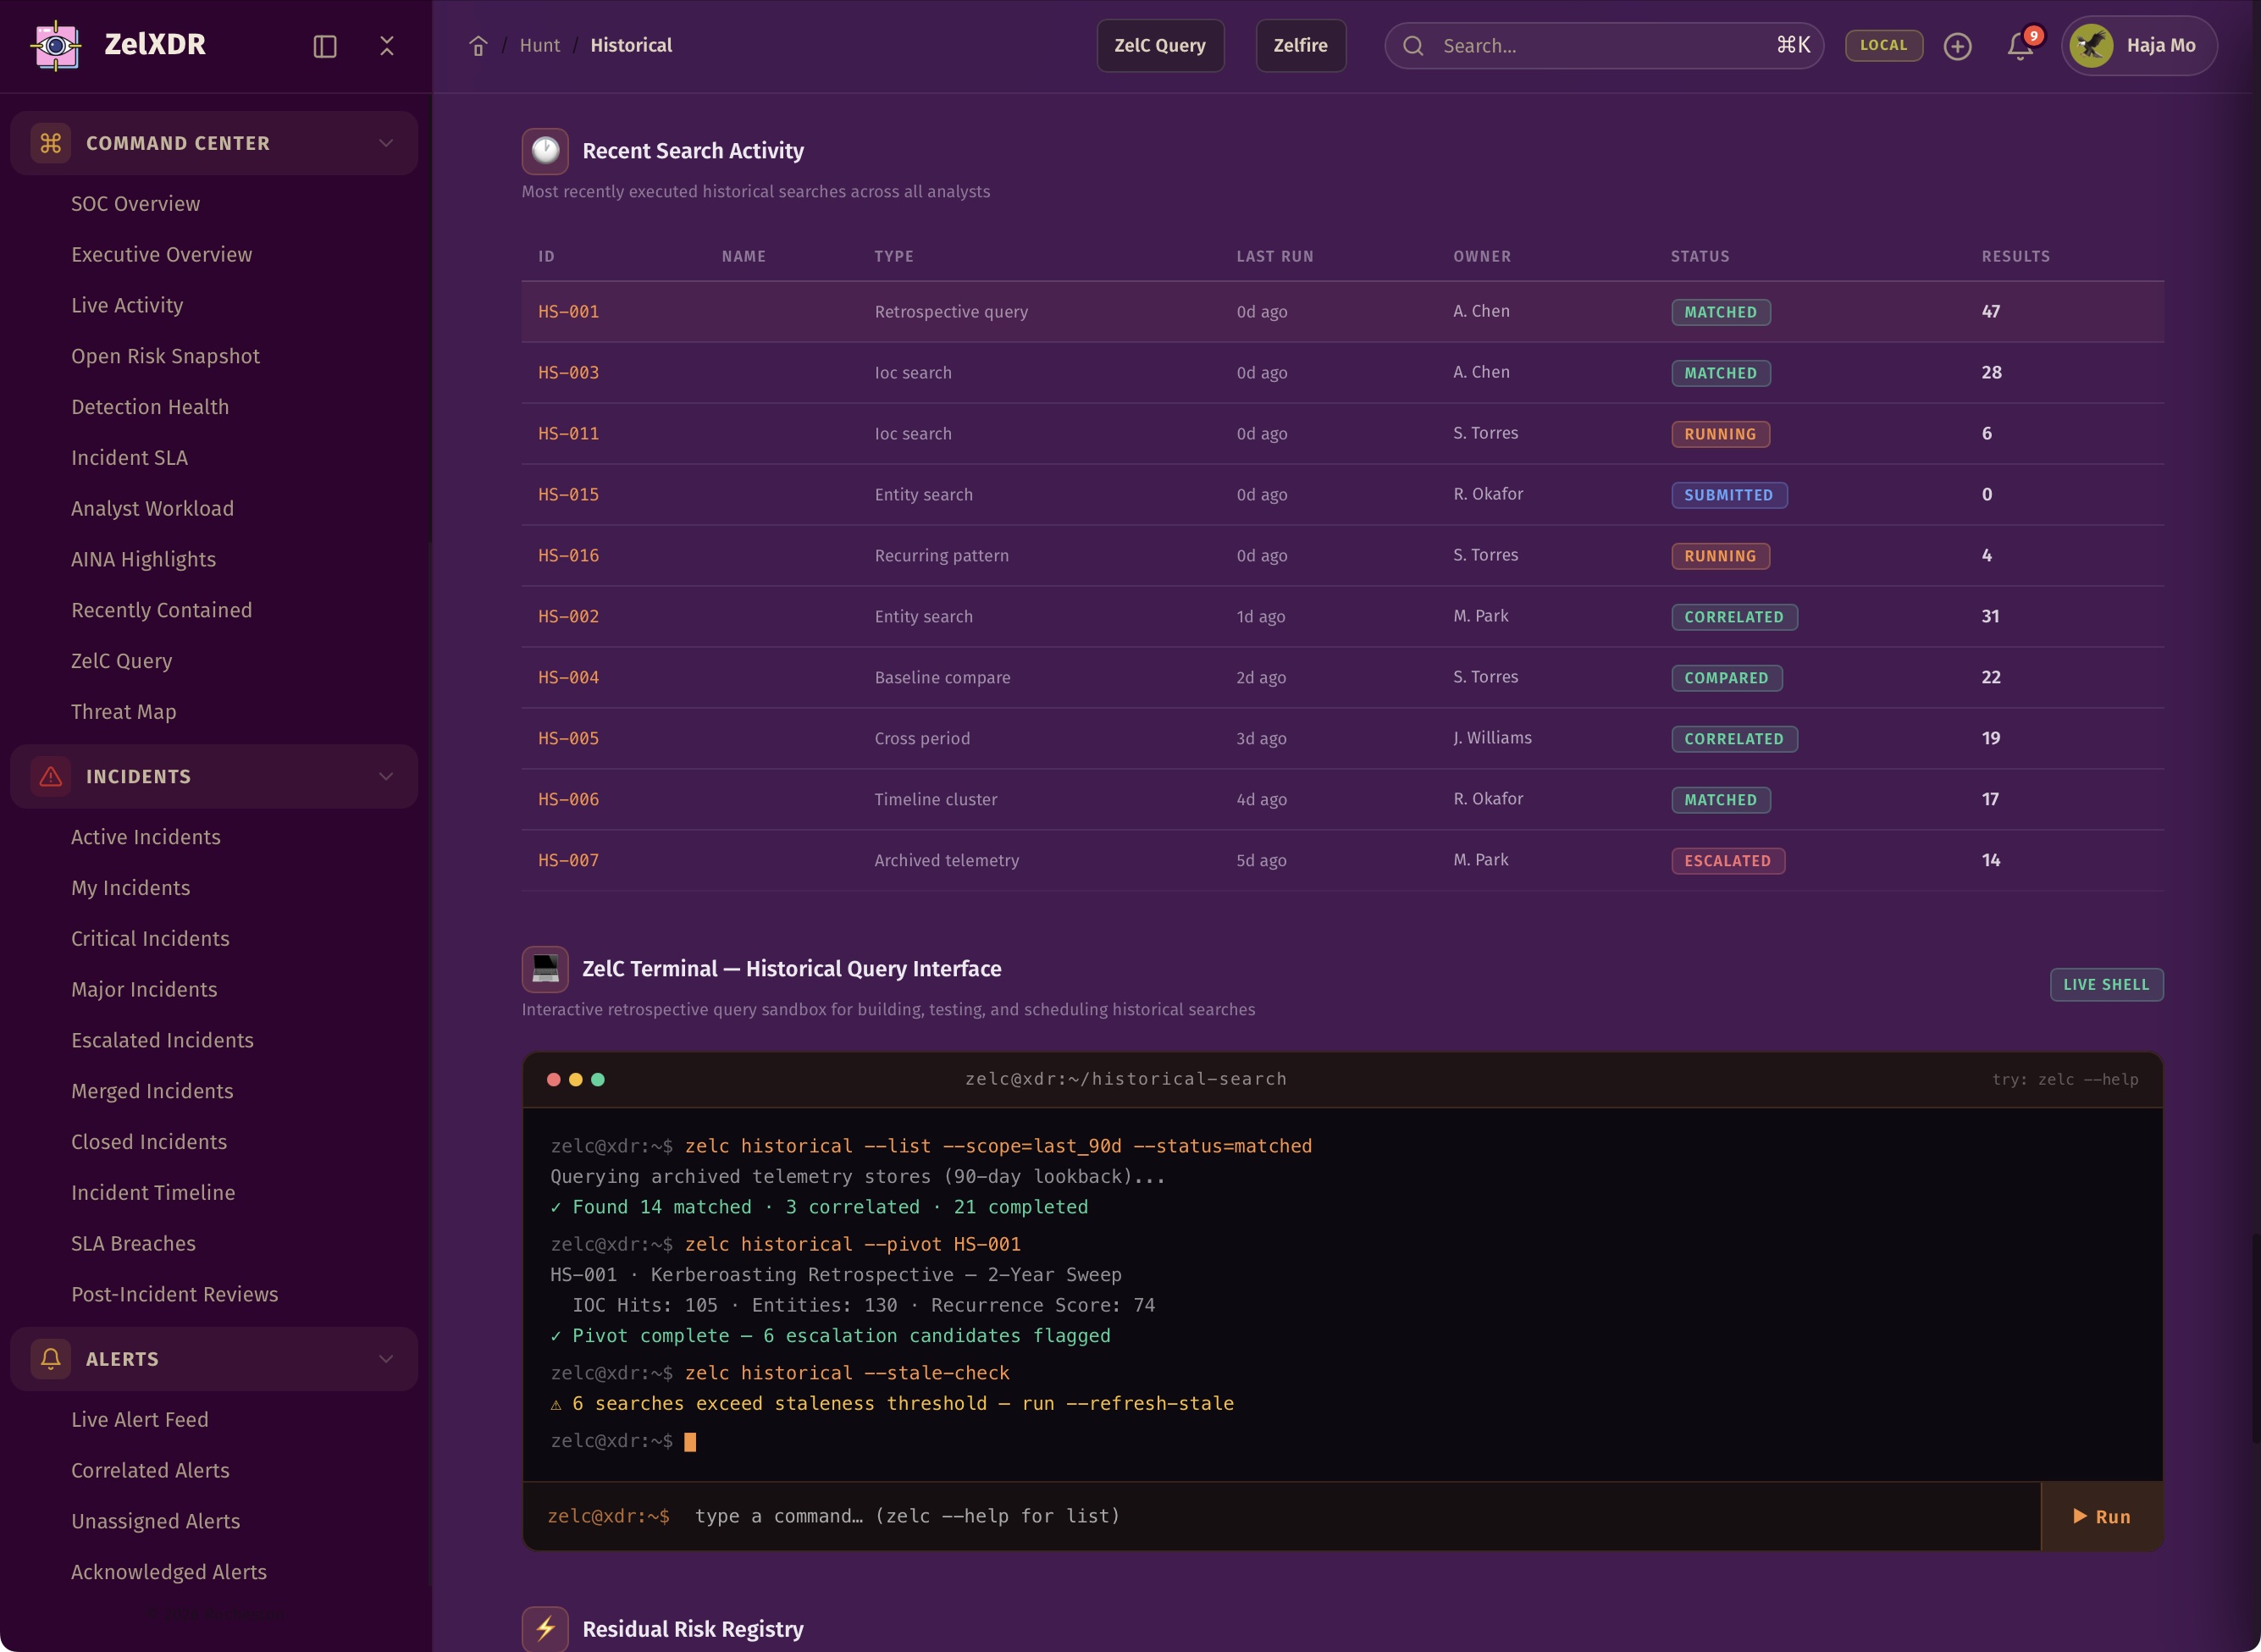
ZelXDR helps teams search past telemetry, archived data, recurring patterns, and long-range behavior to uncover older signals that still matter today.
The past often explains the present.
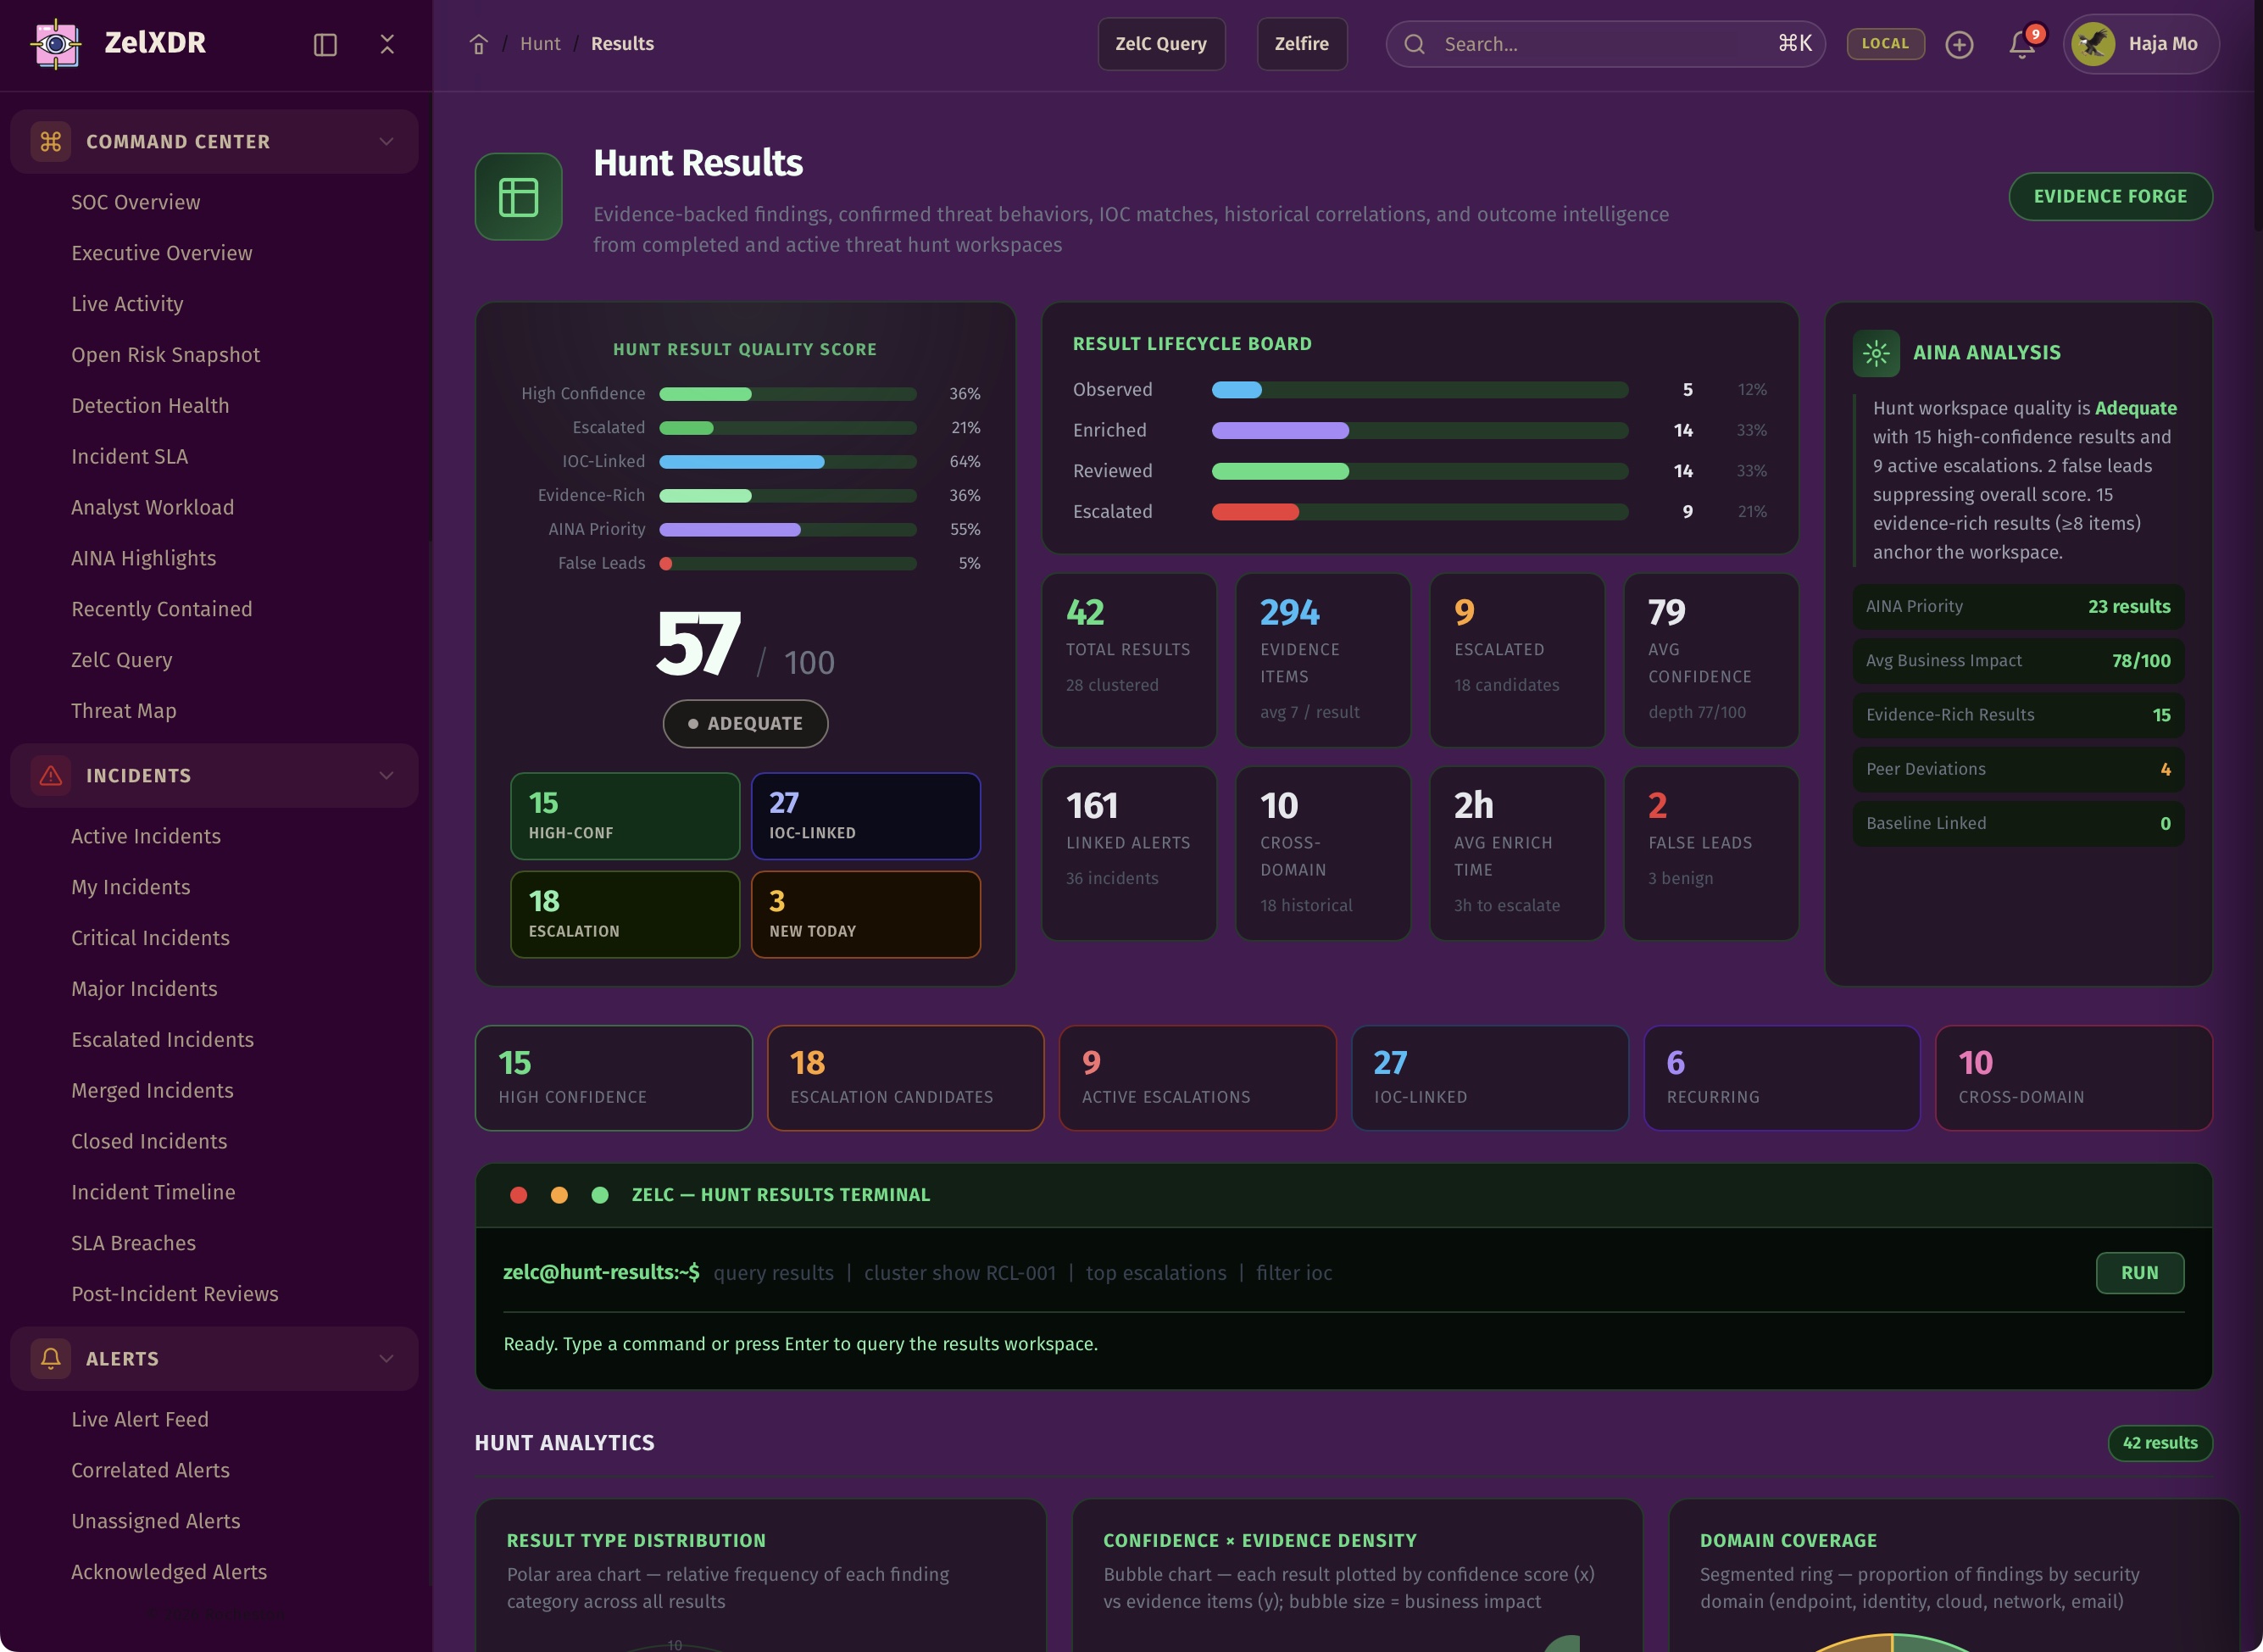
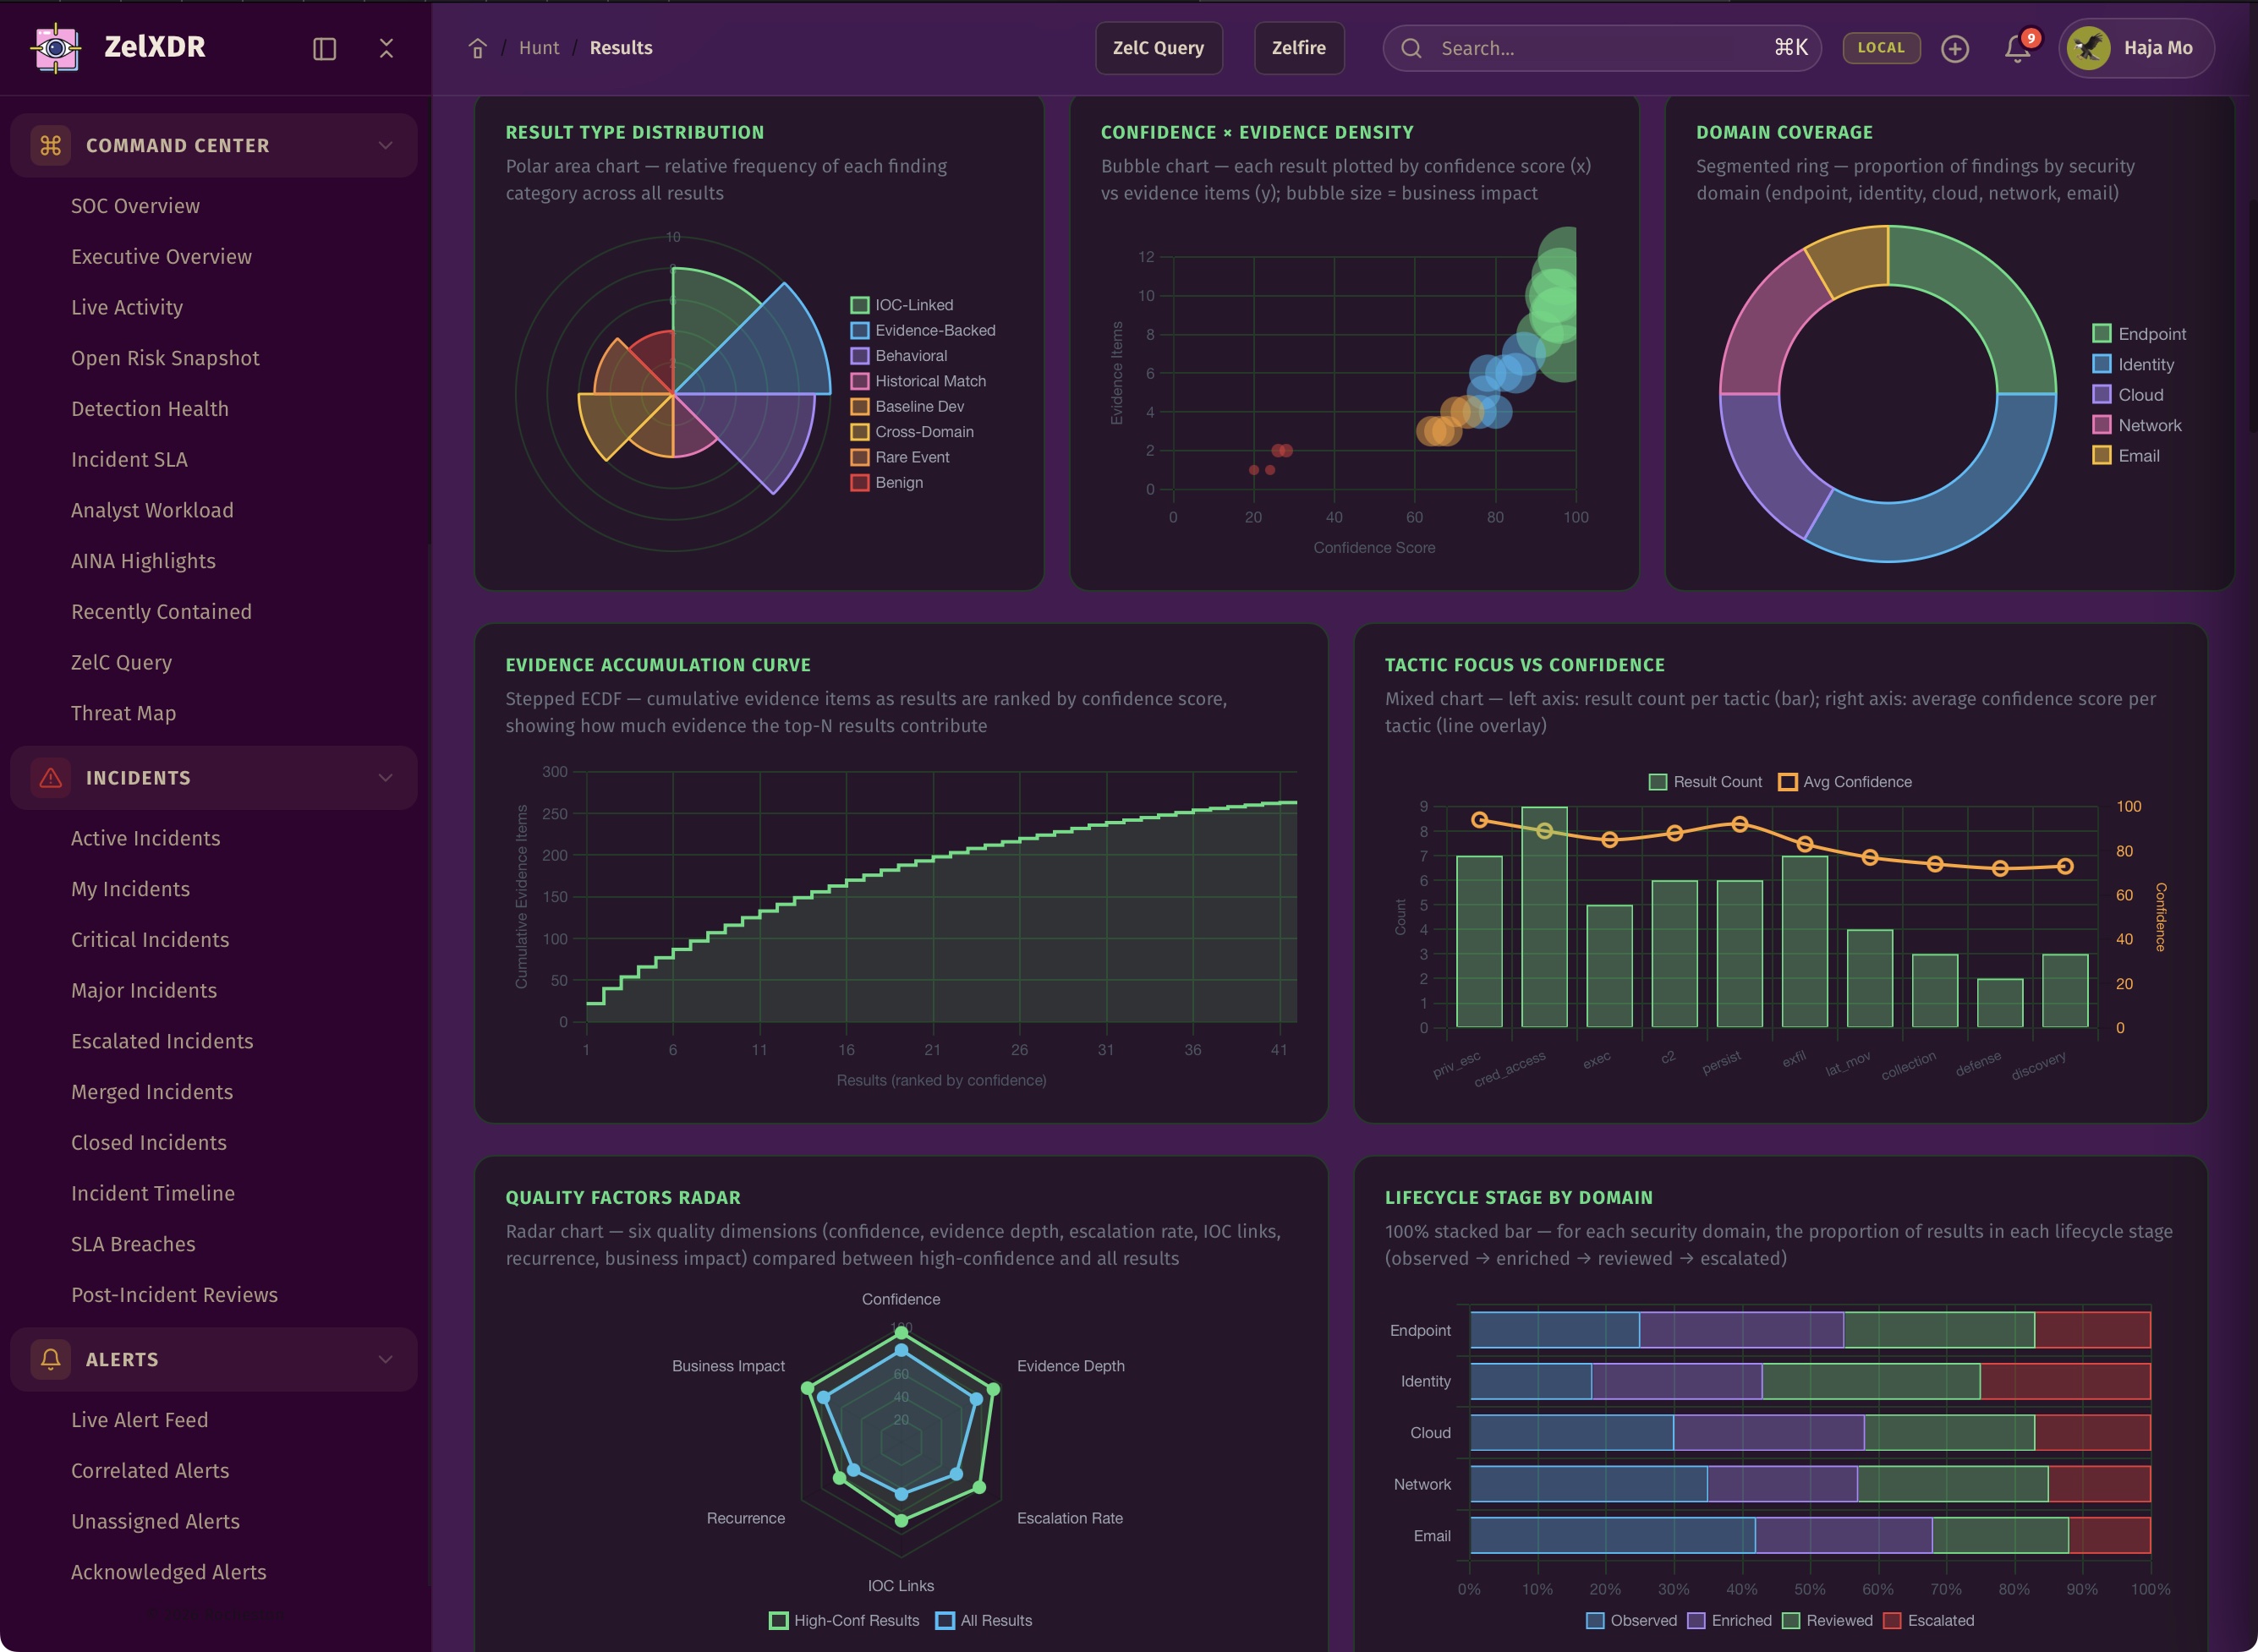
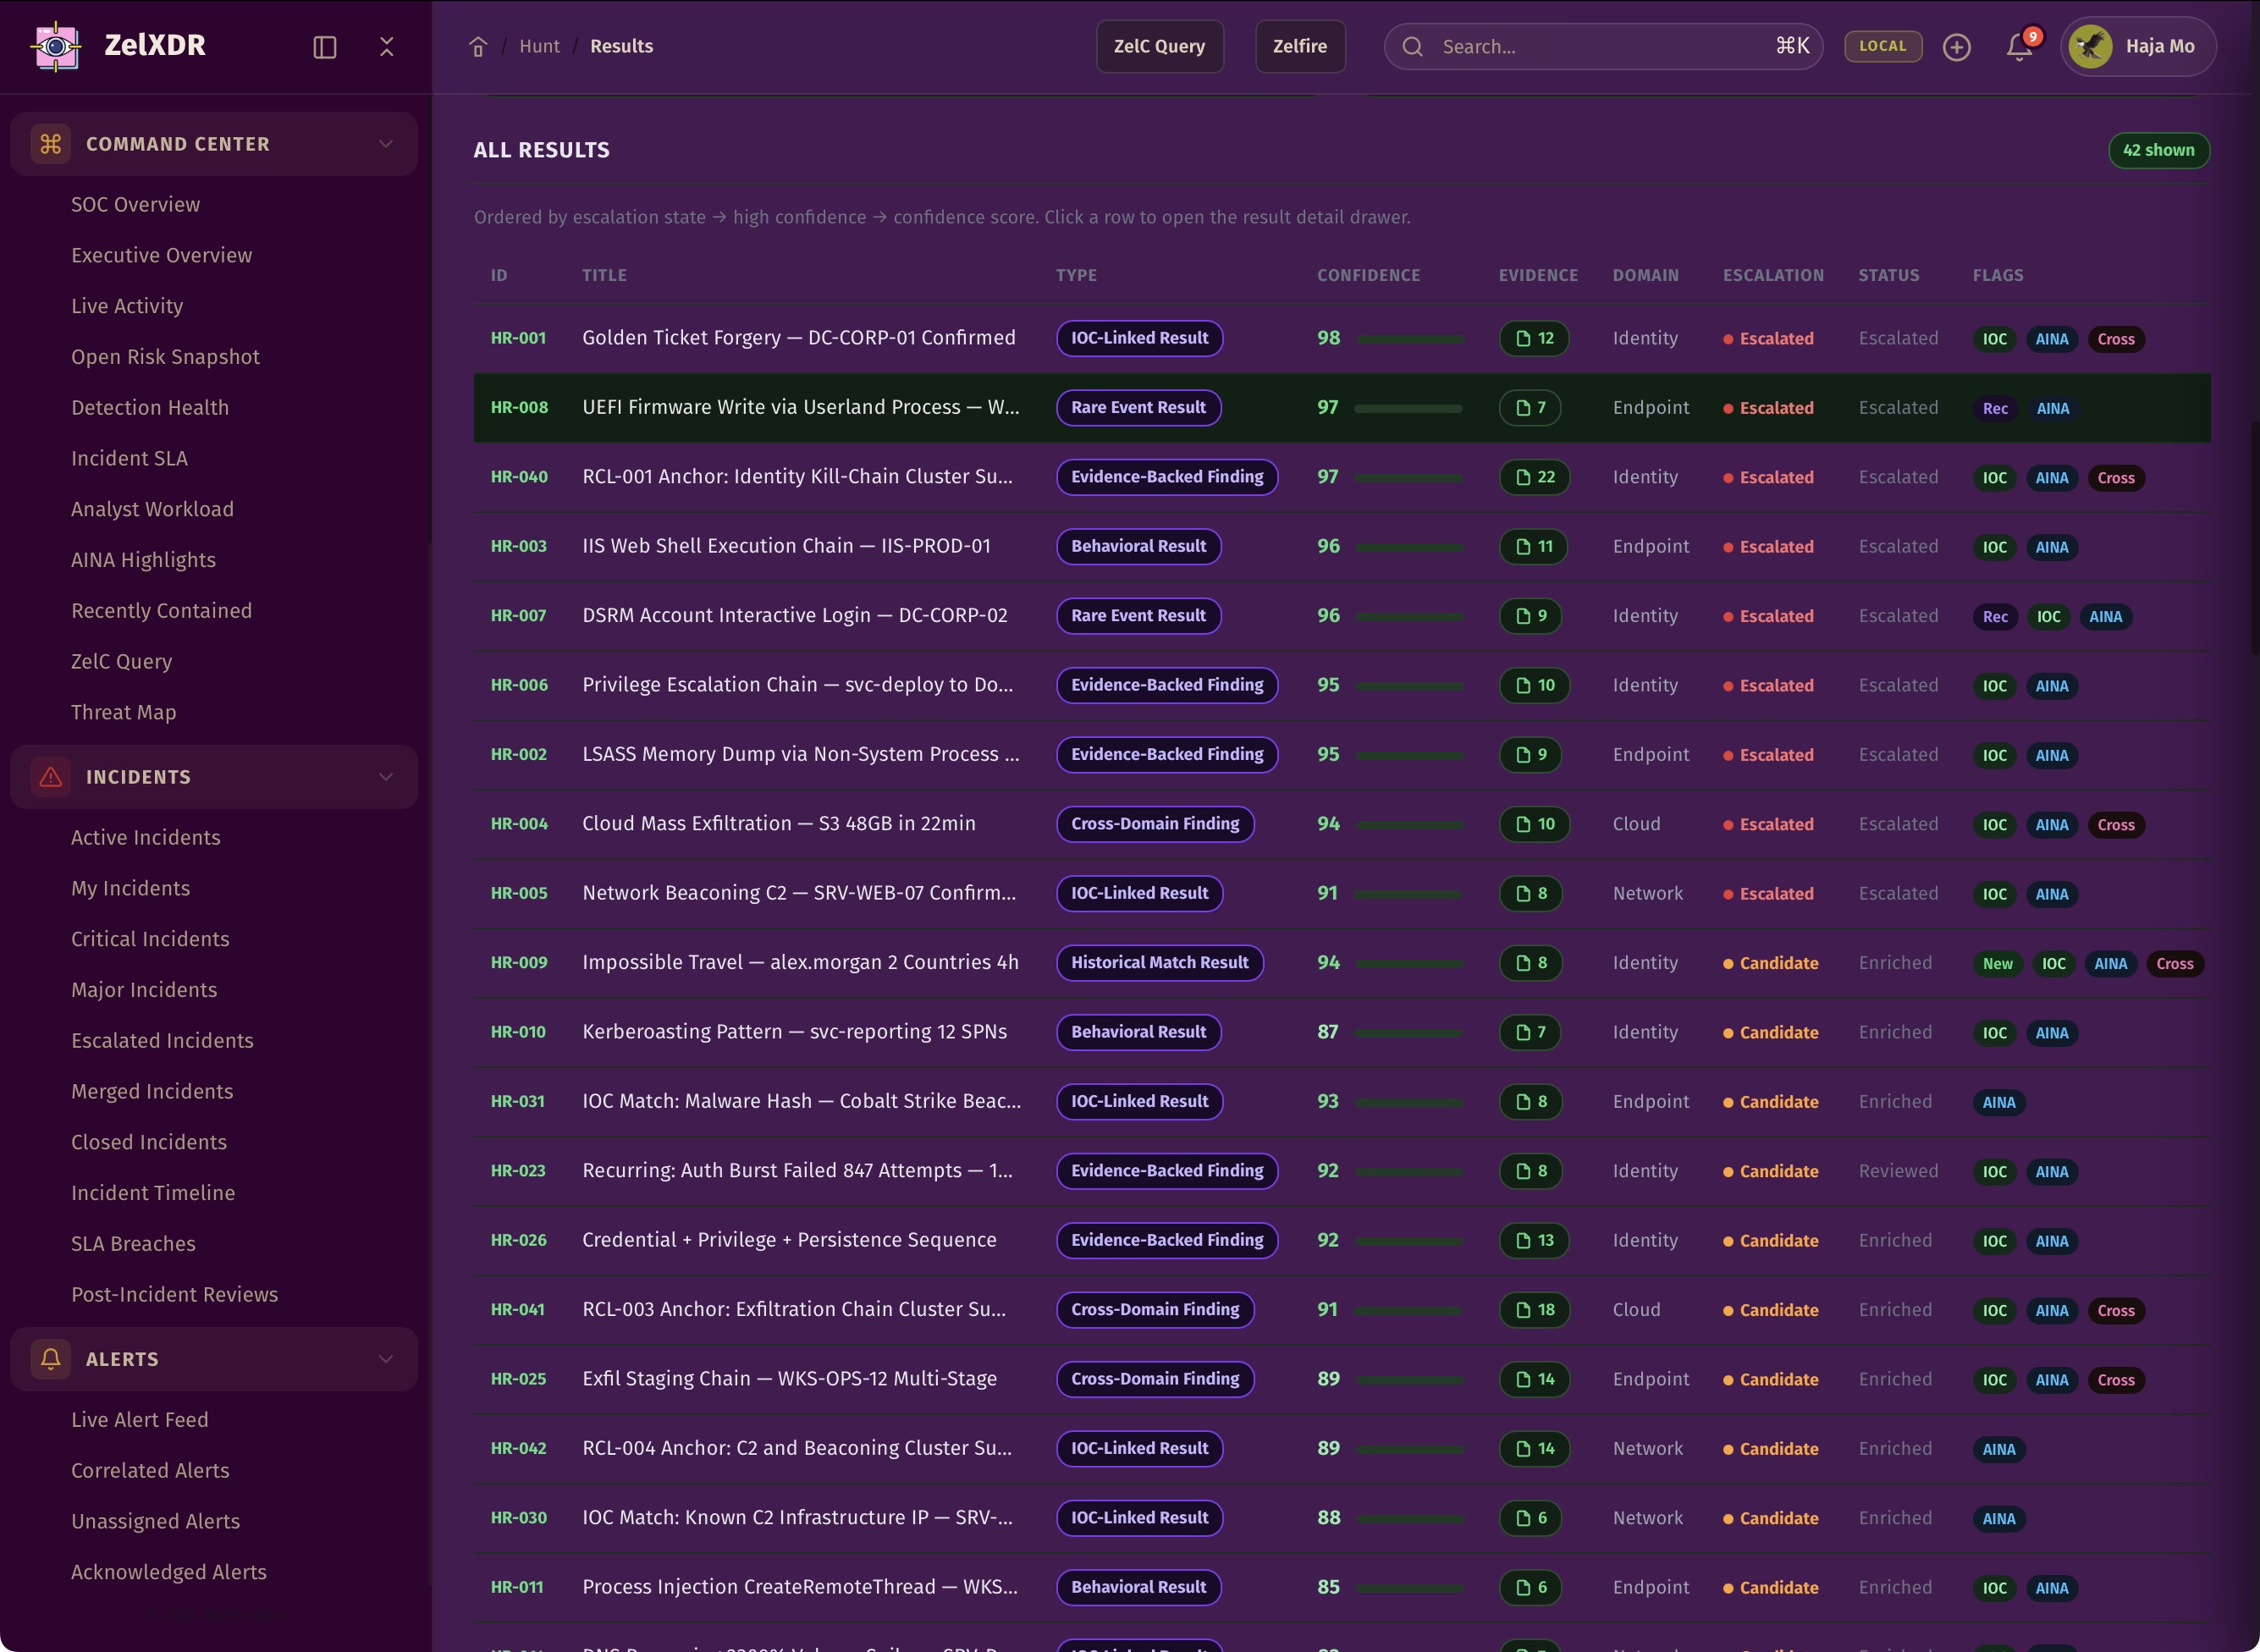
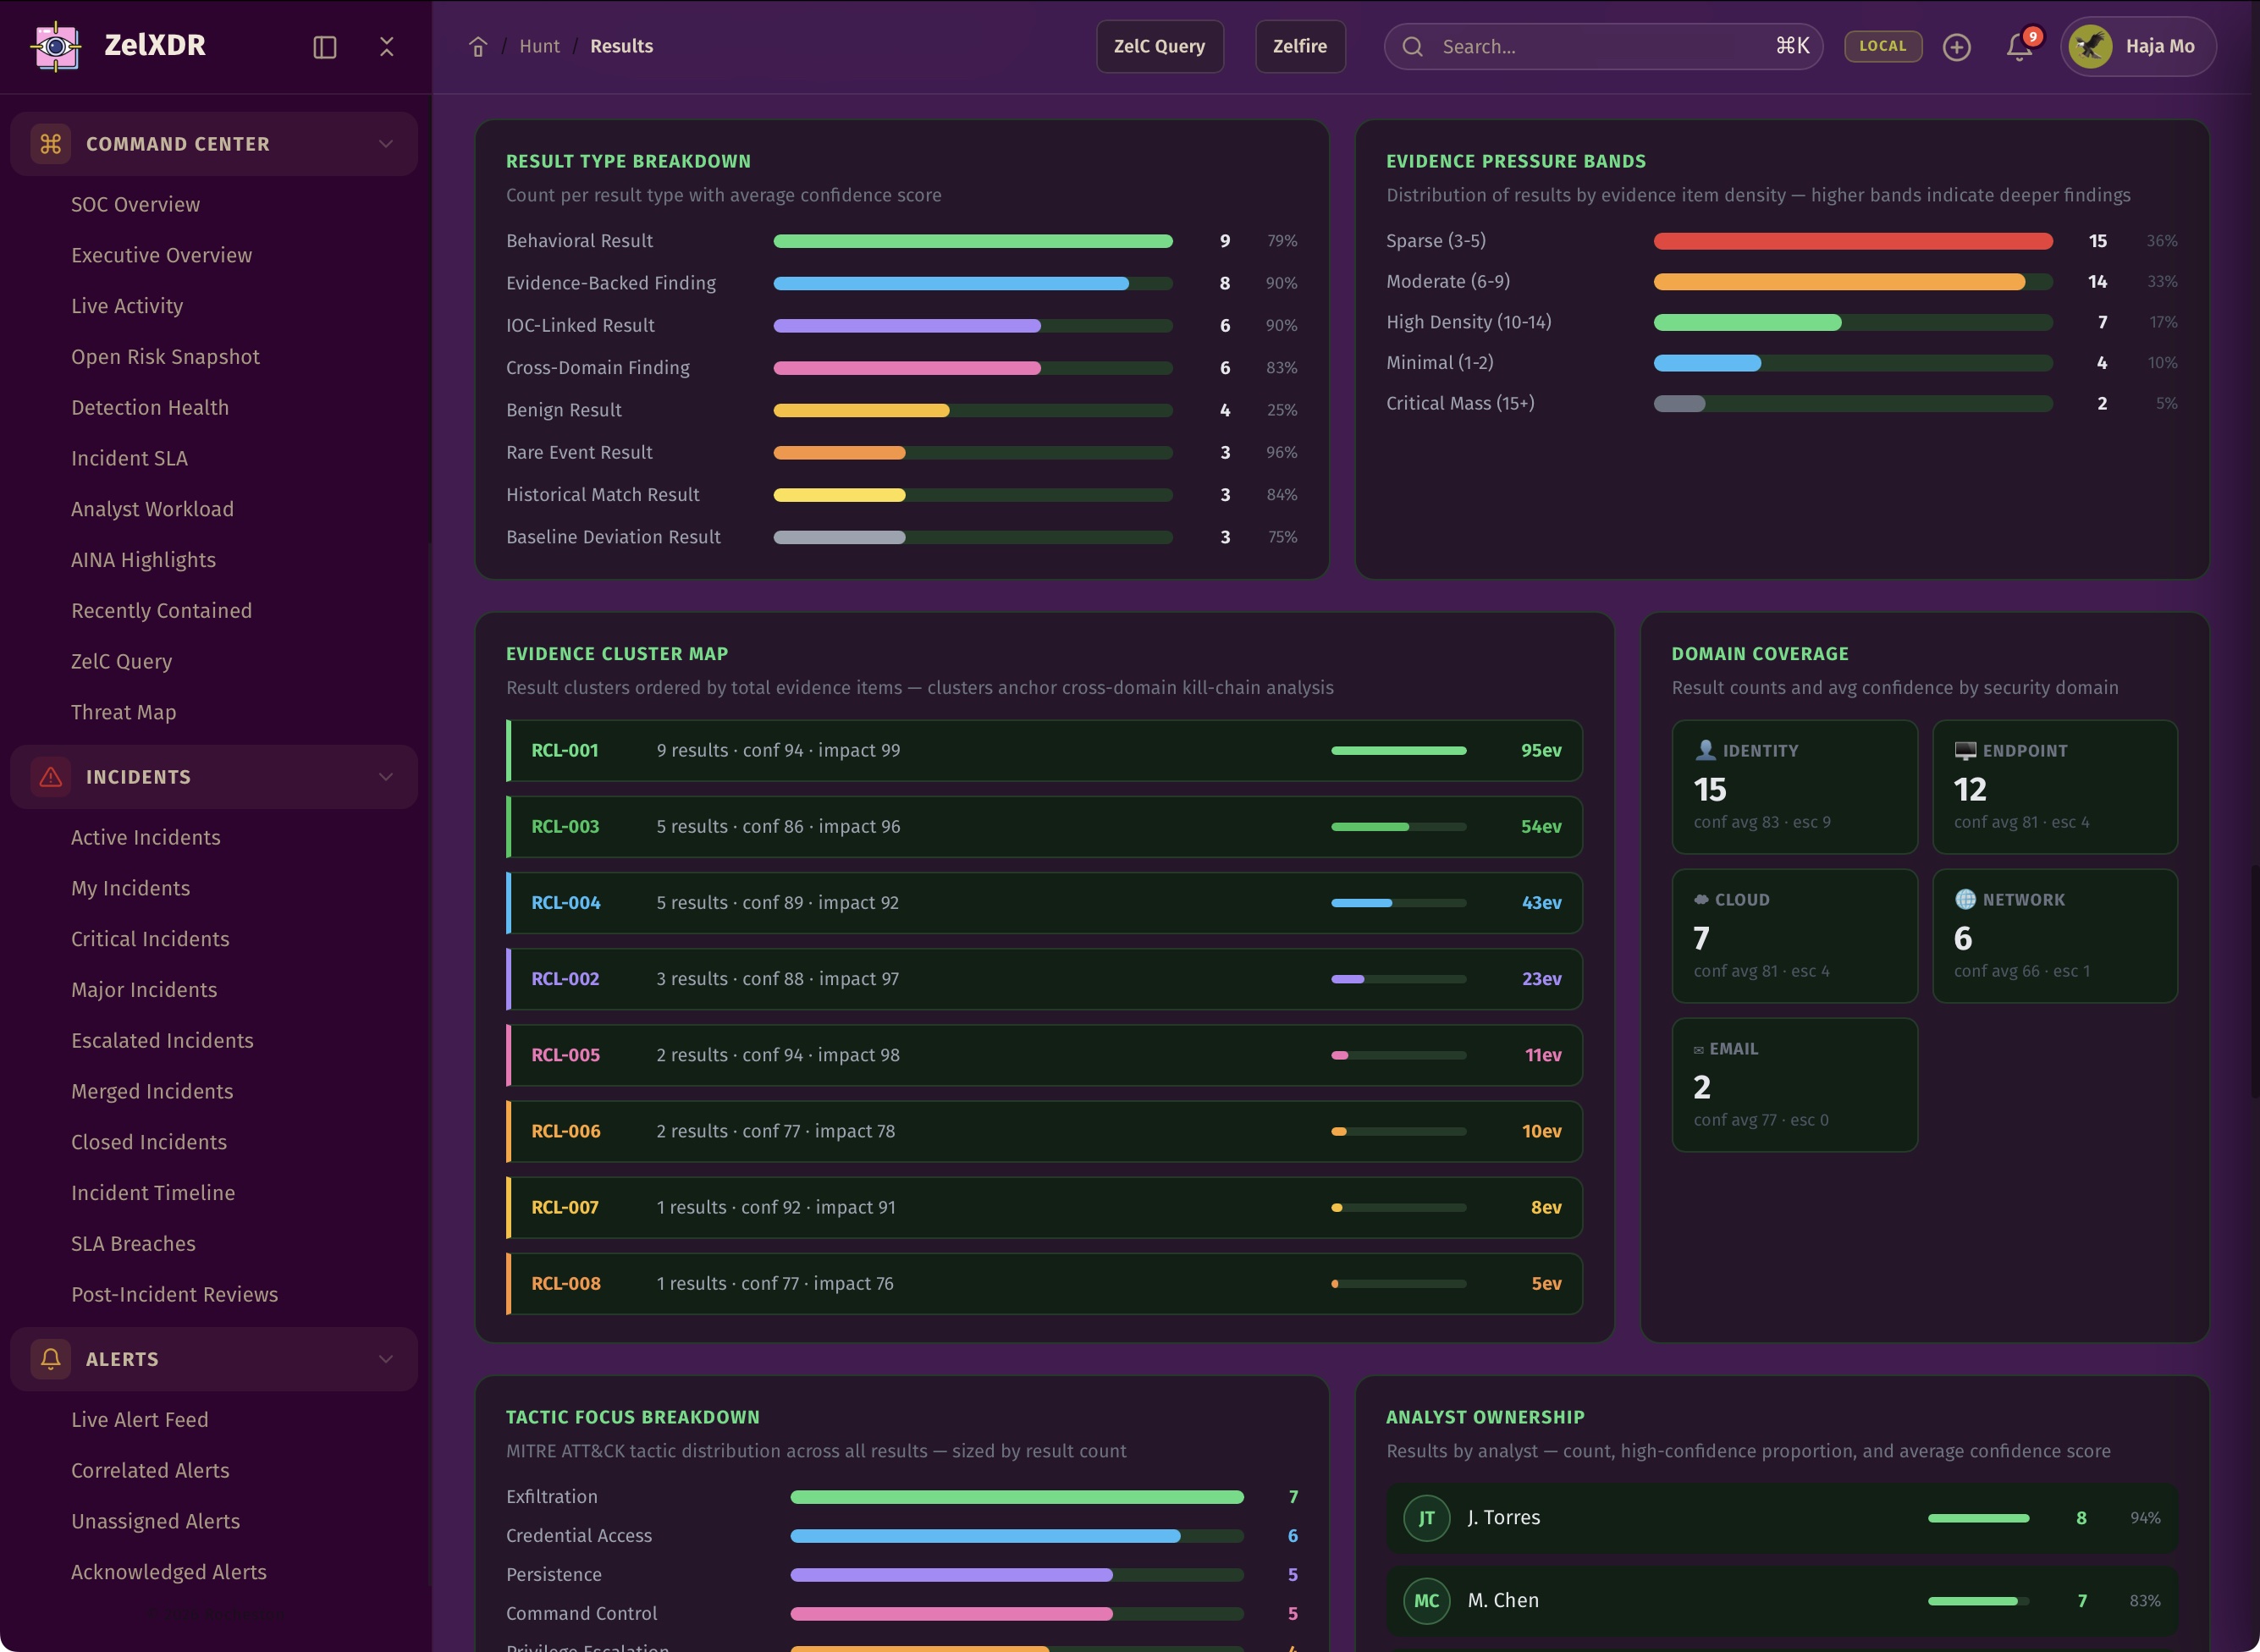
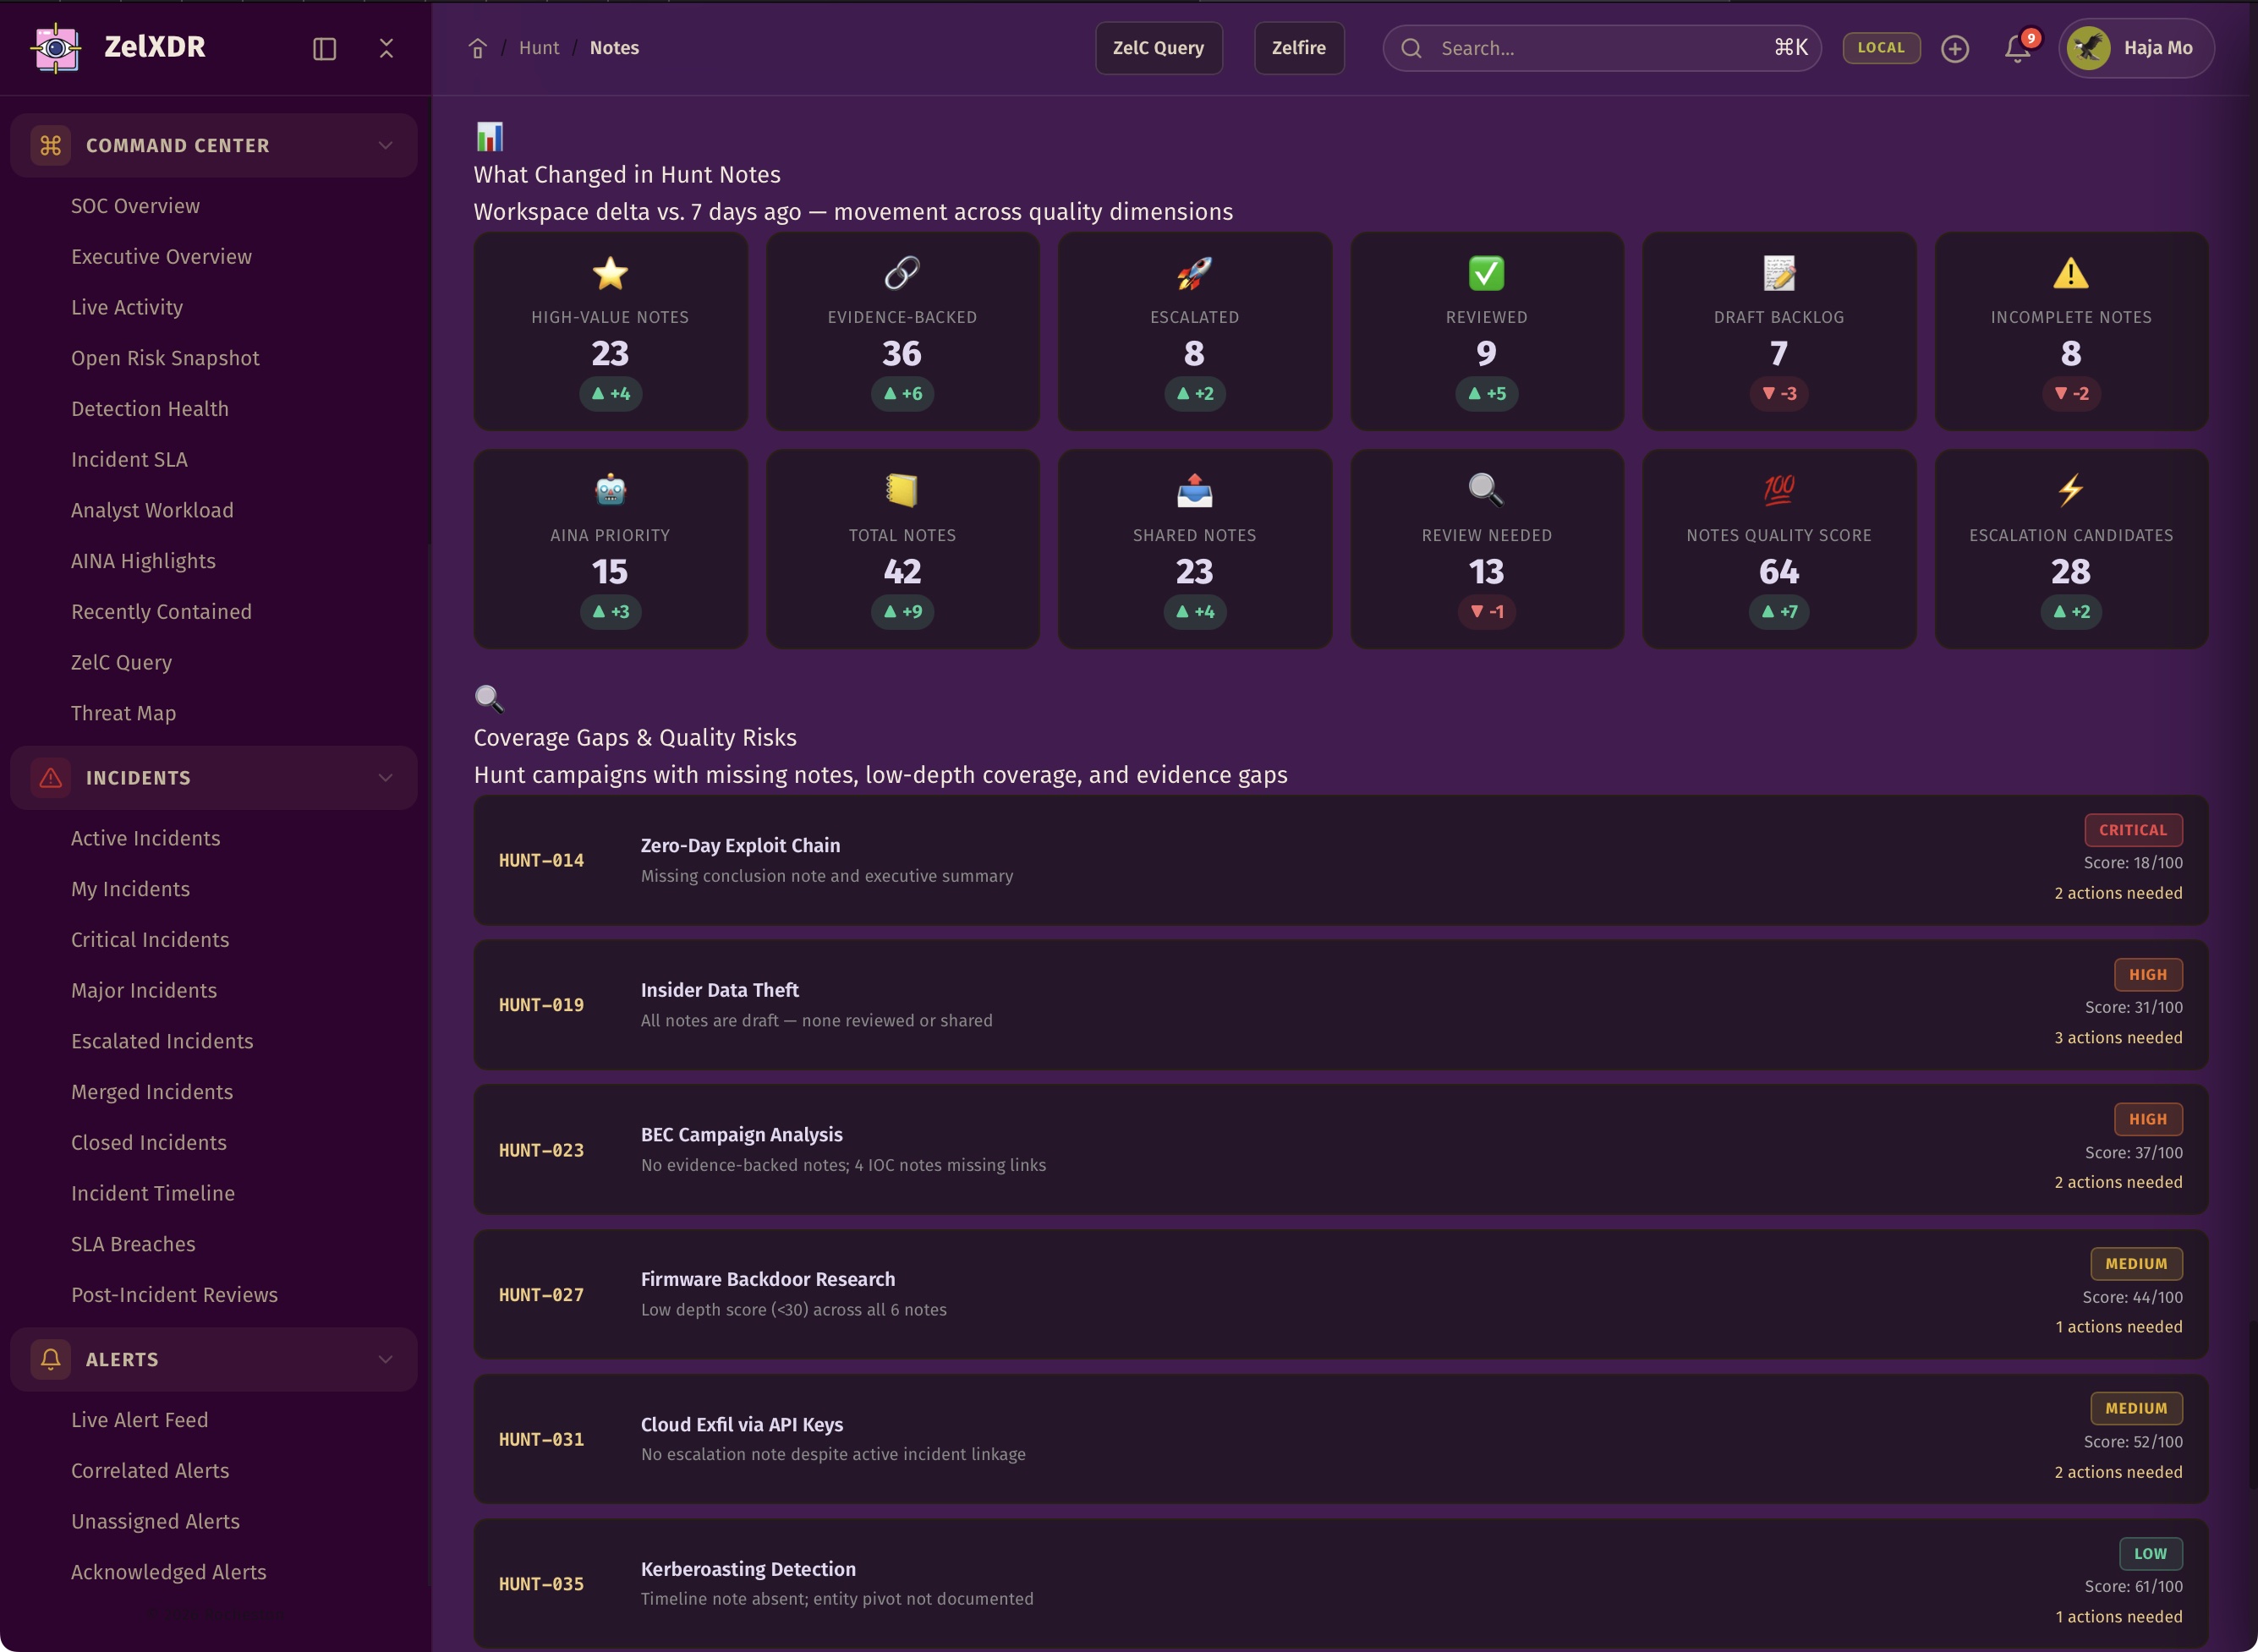
ZelXDR captures hunt outcomes, evidence-backed results, clustered findings, and escalation candidates so analysts can move from discovery to action with structure and confidence.
A result matters only when it changes the next move.
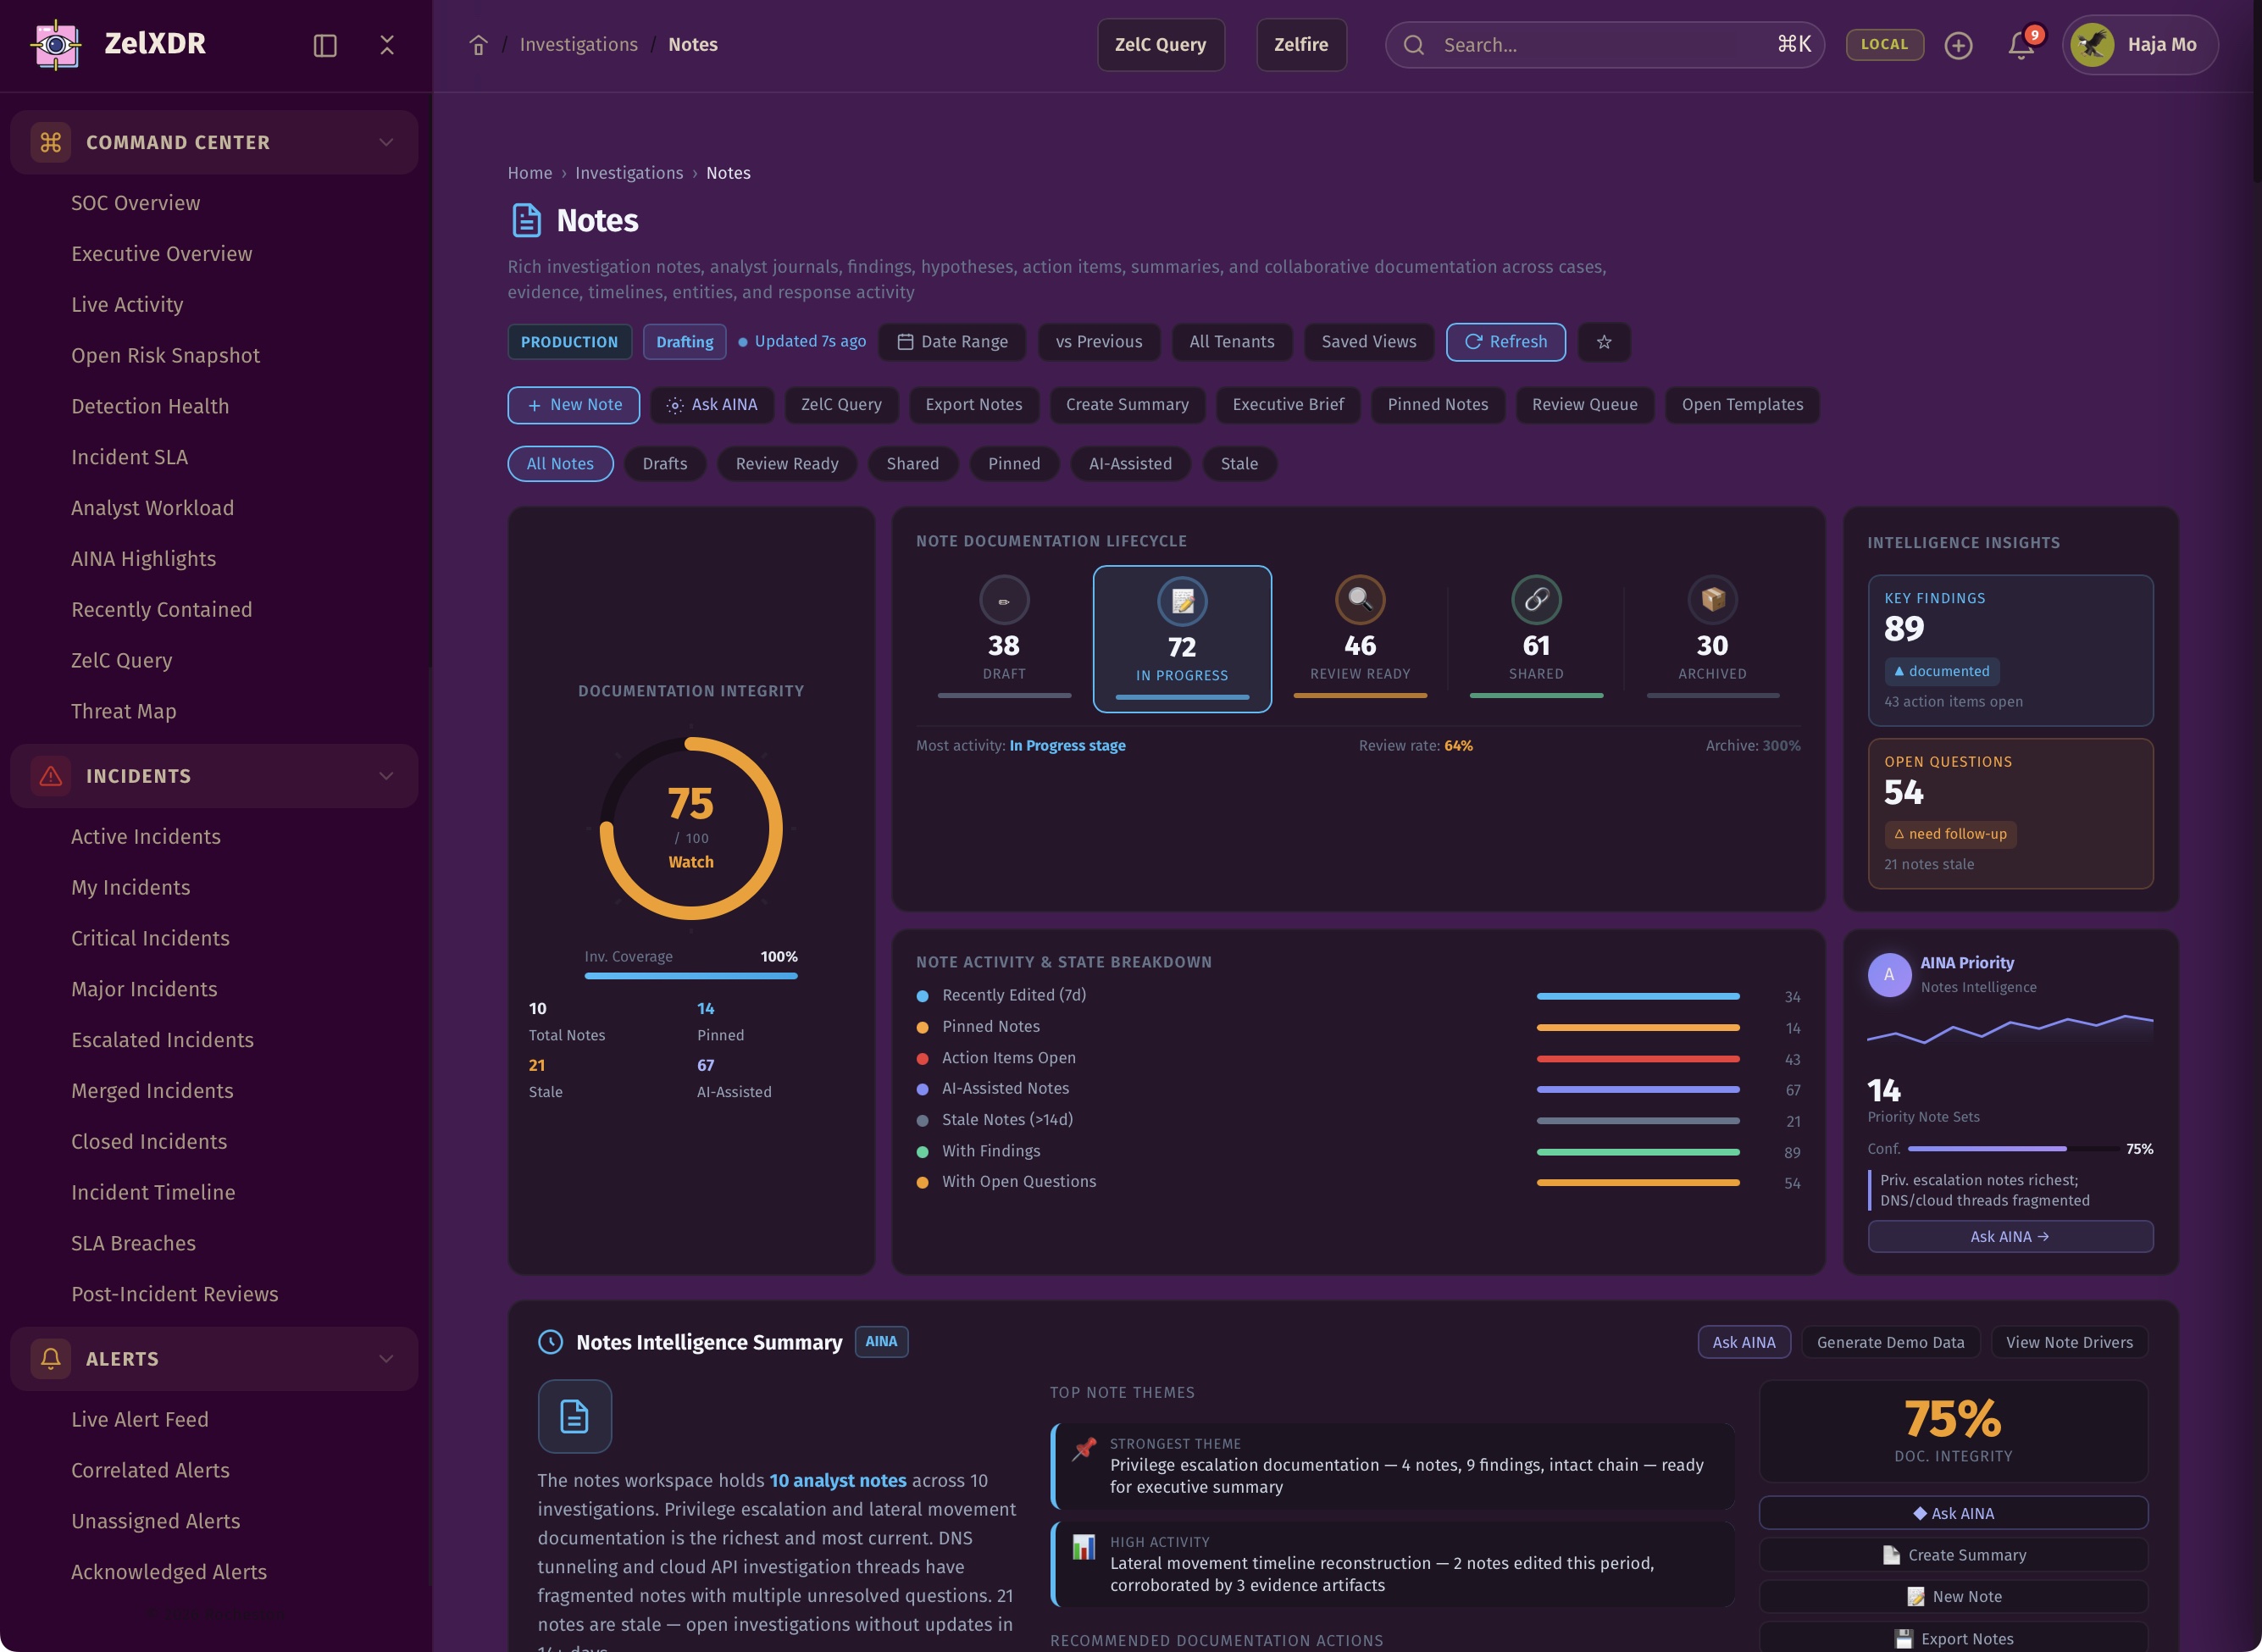
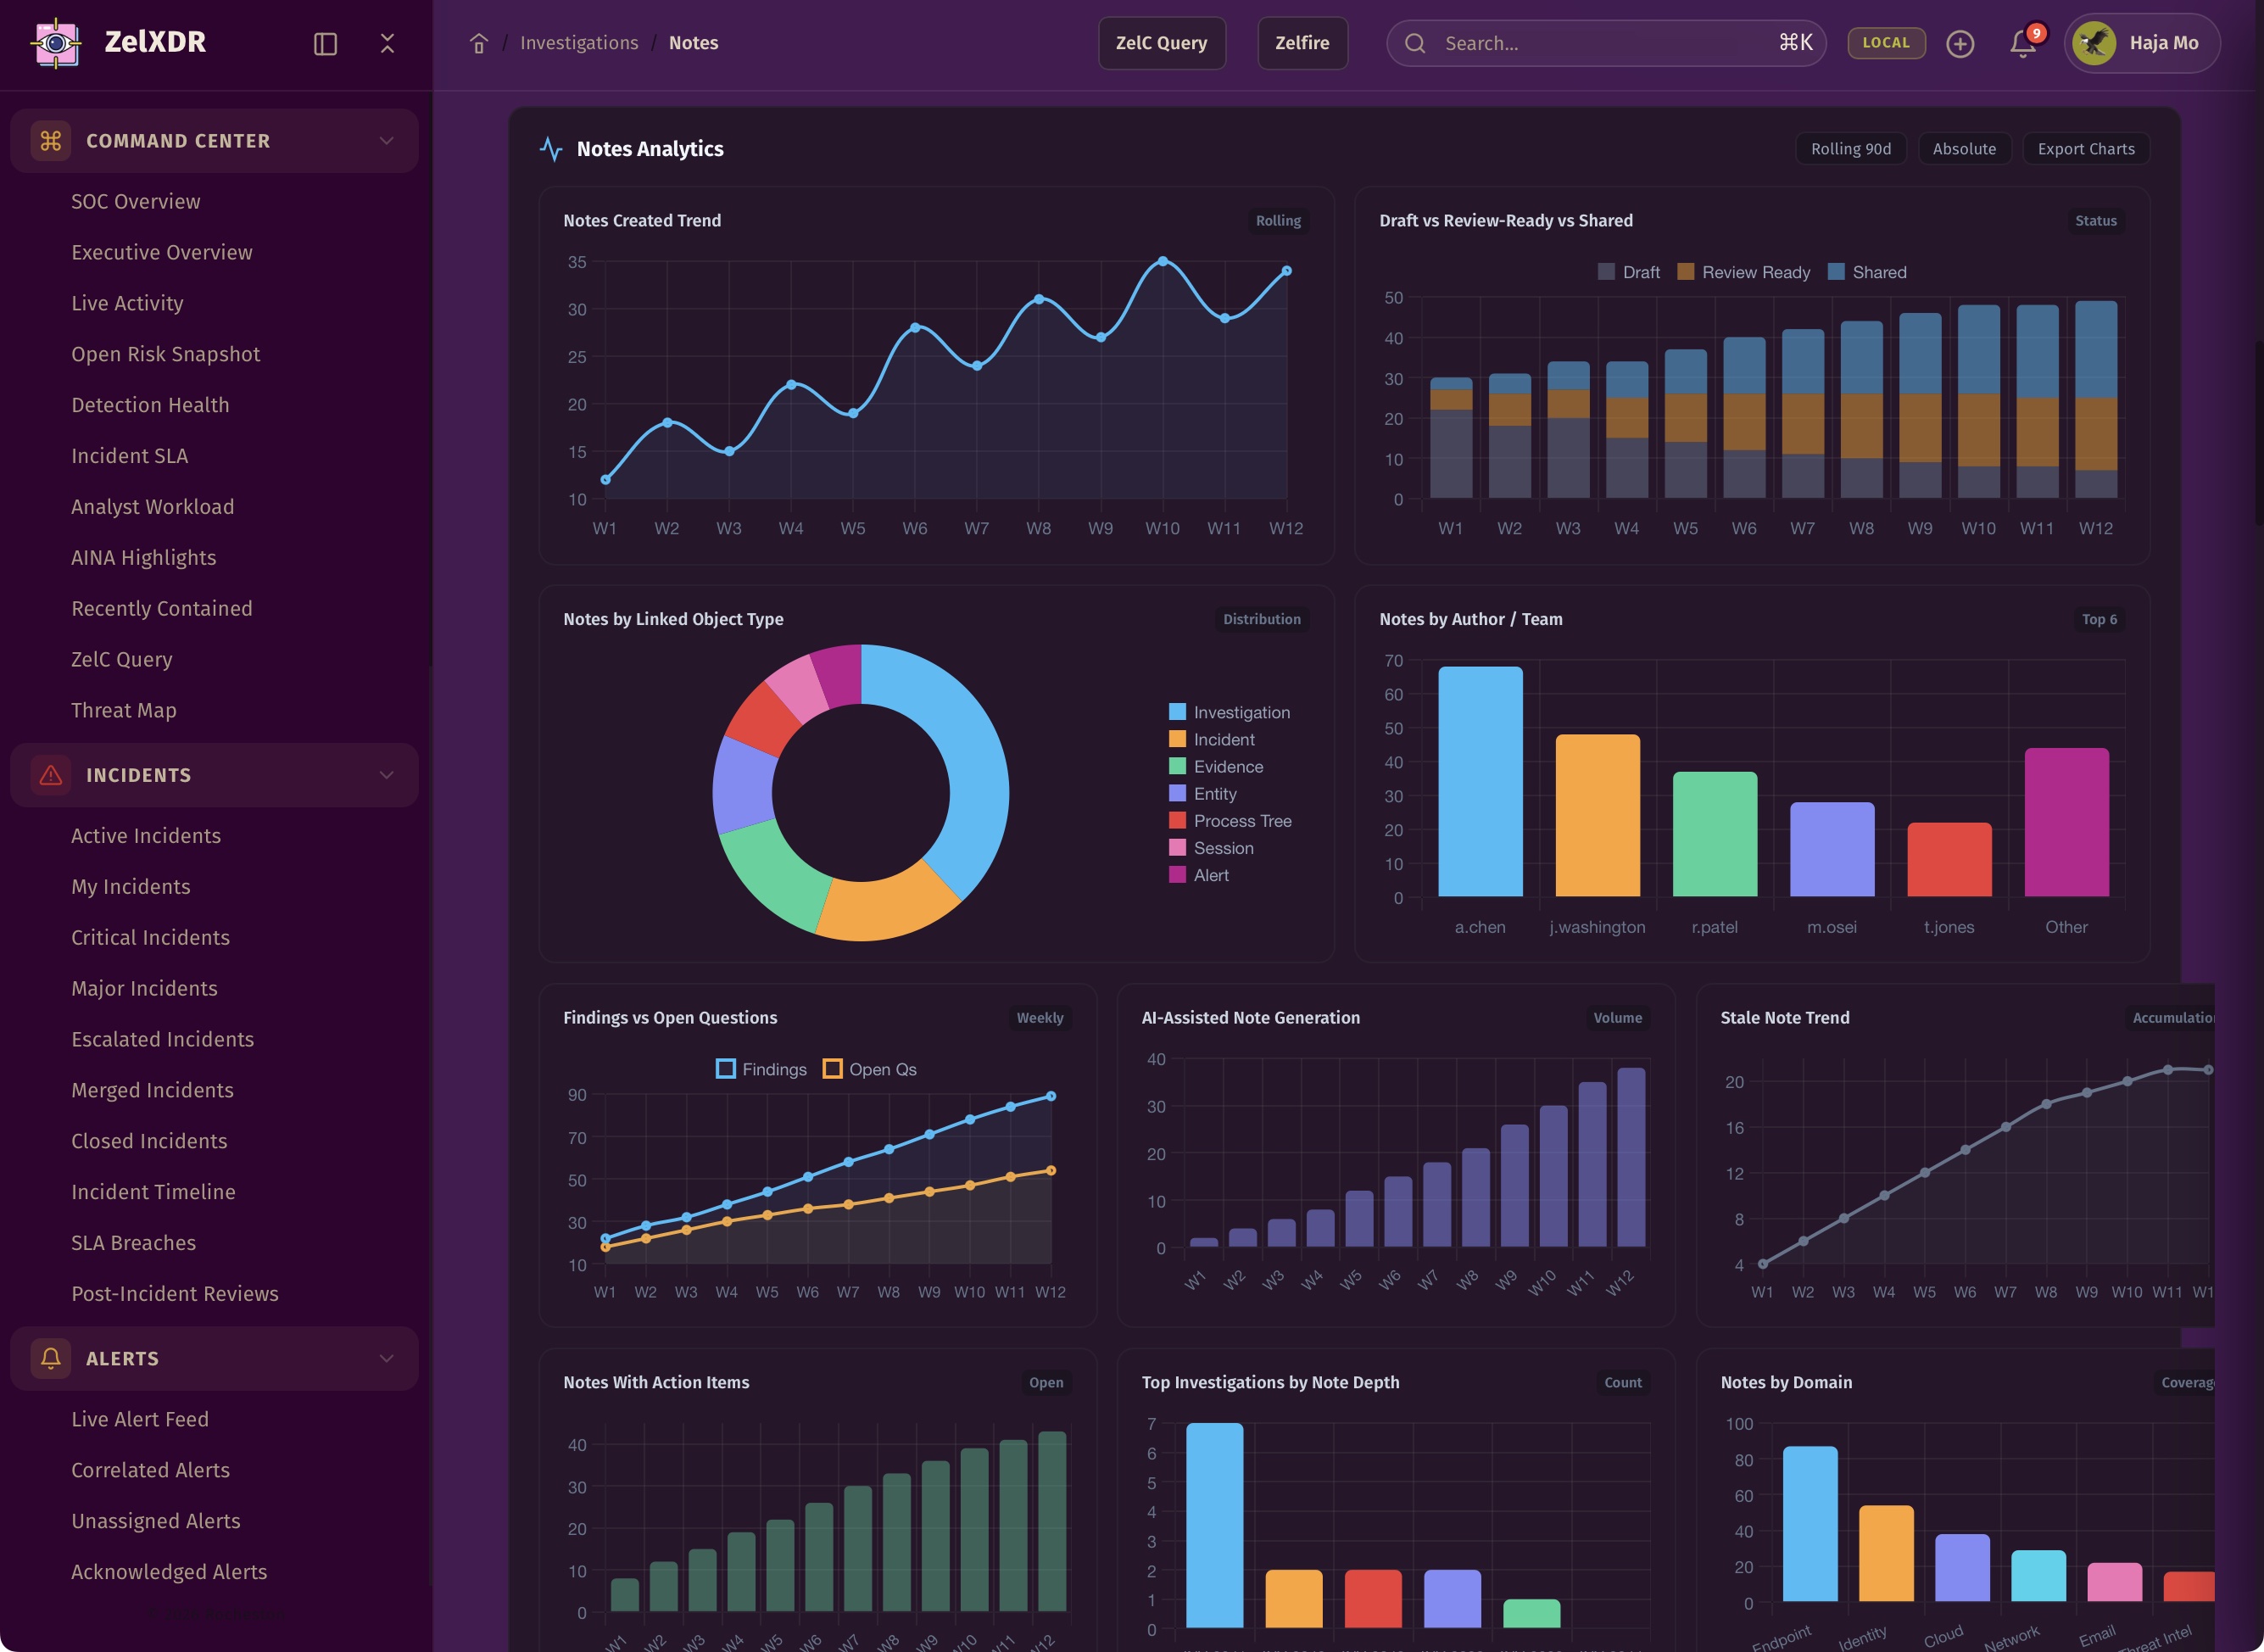
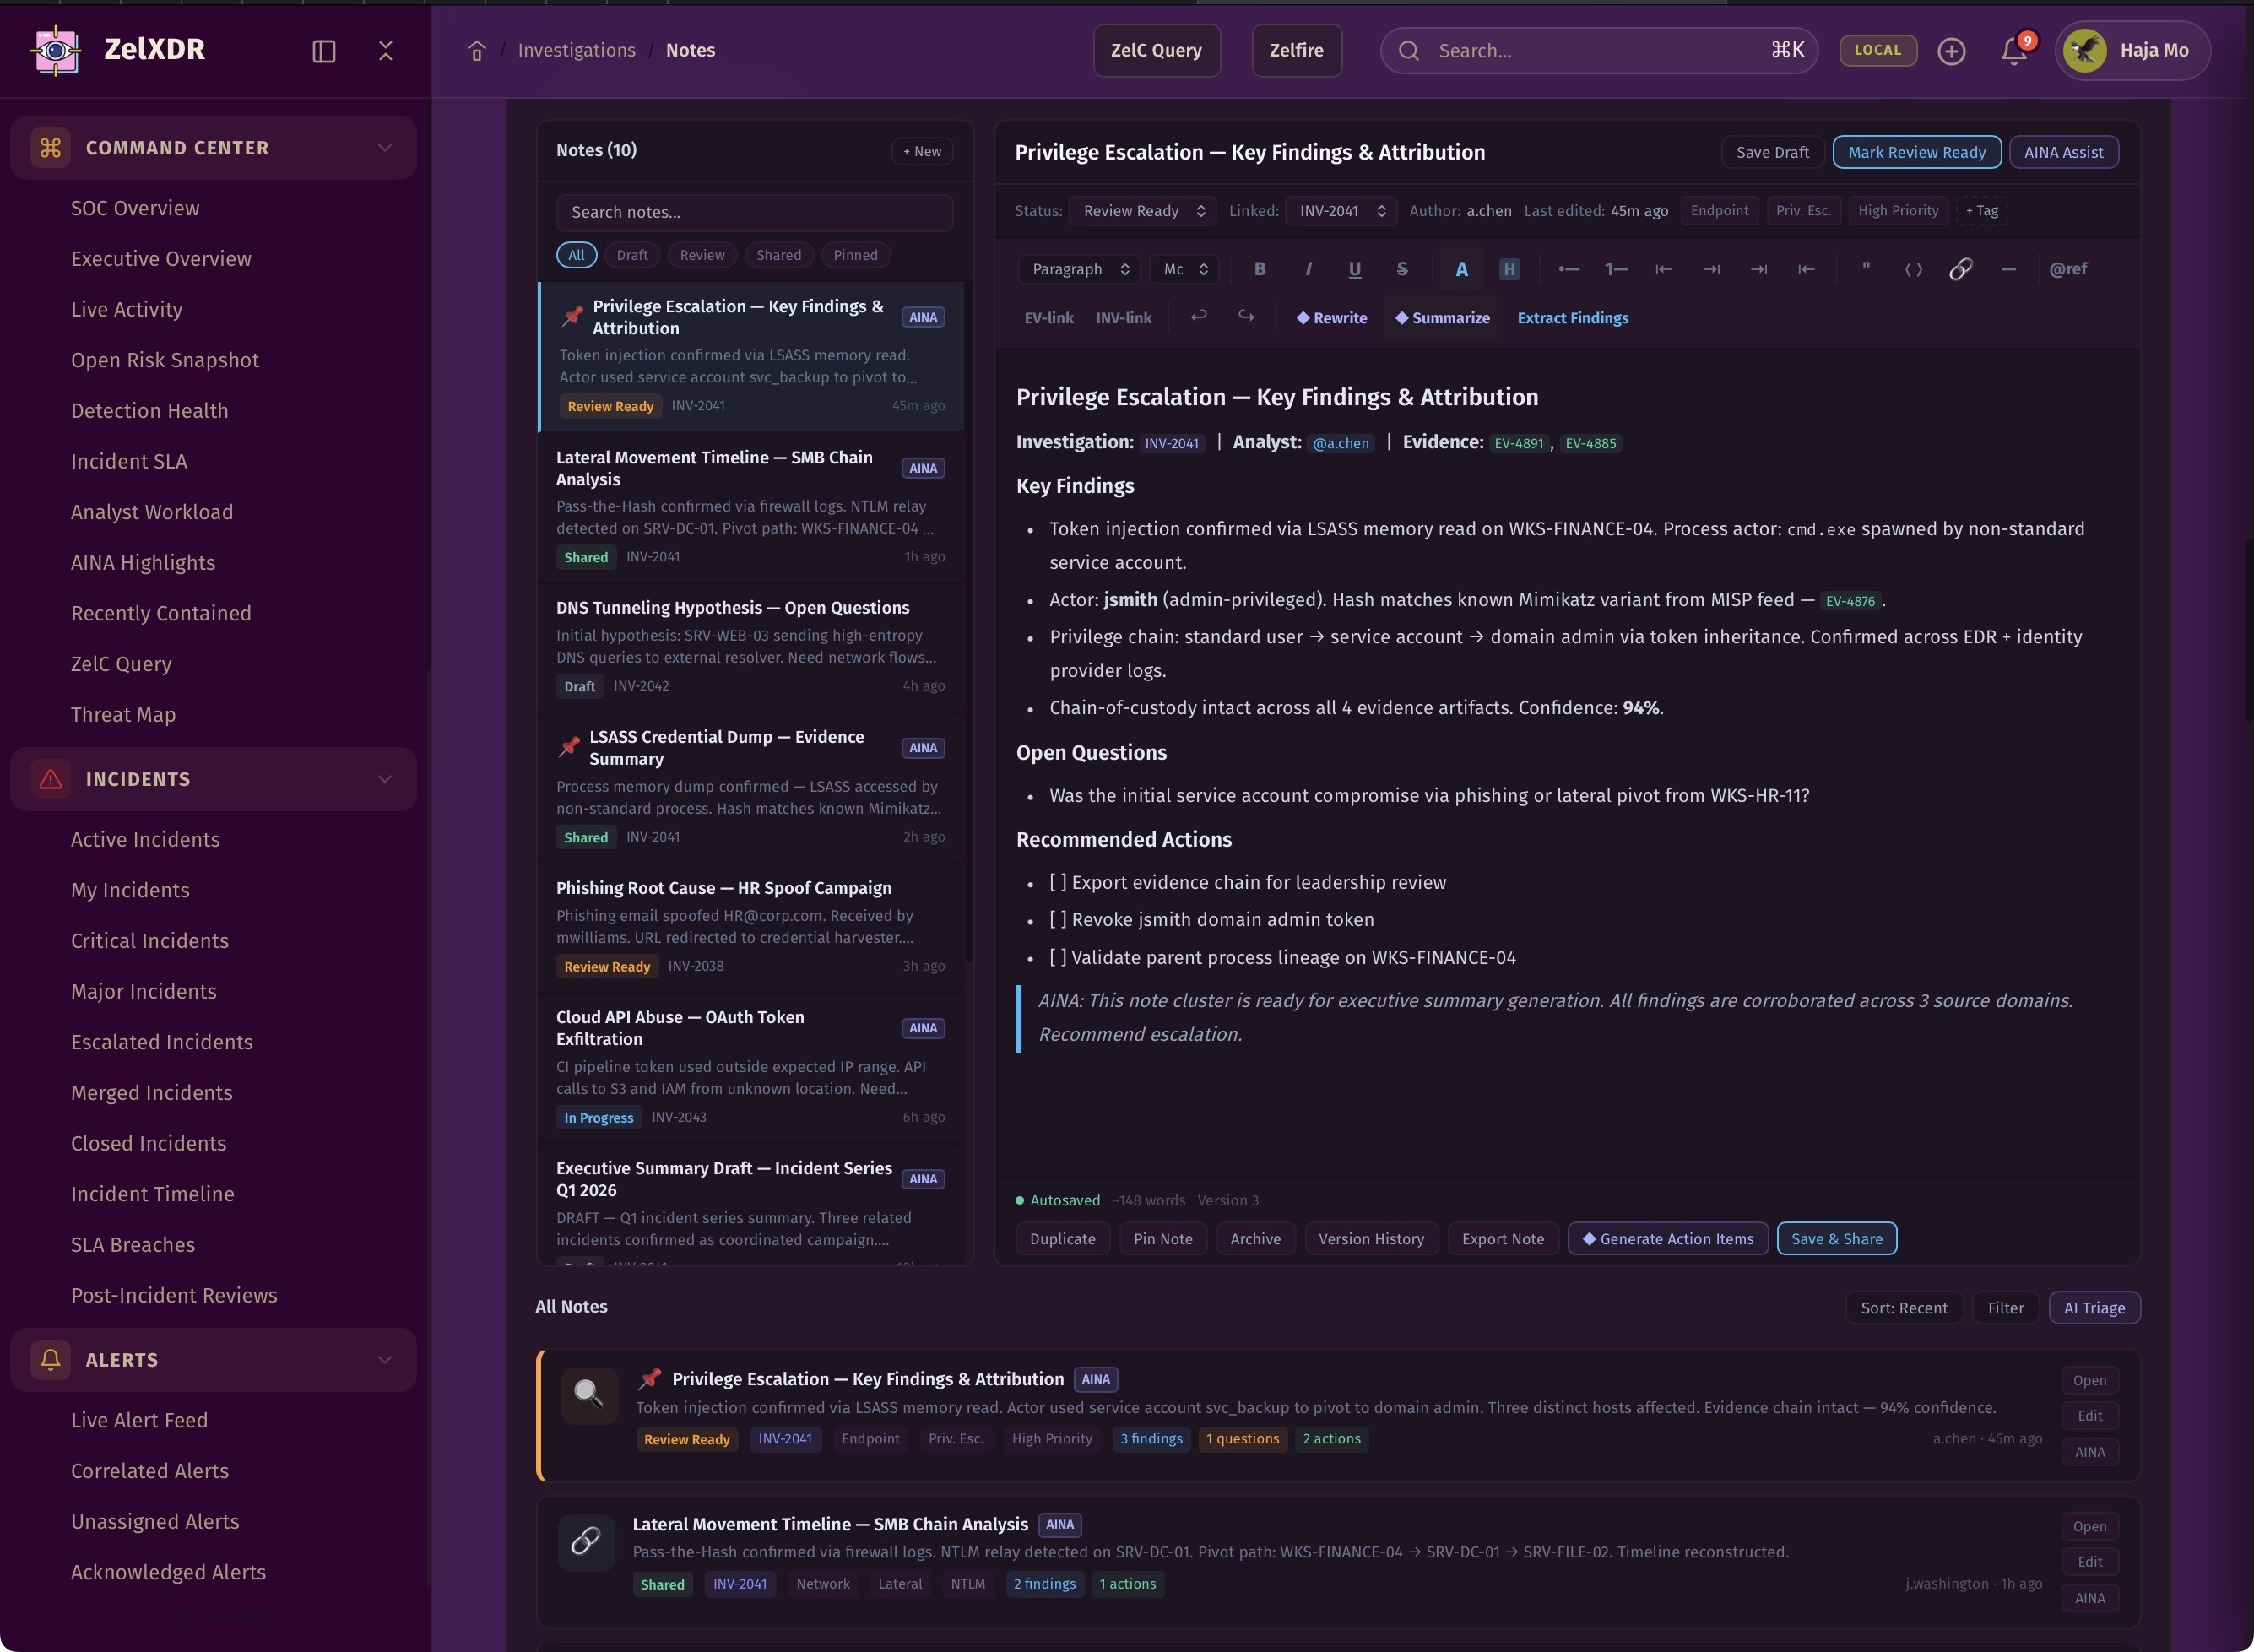
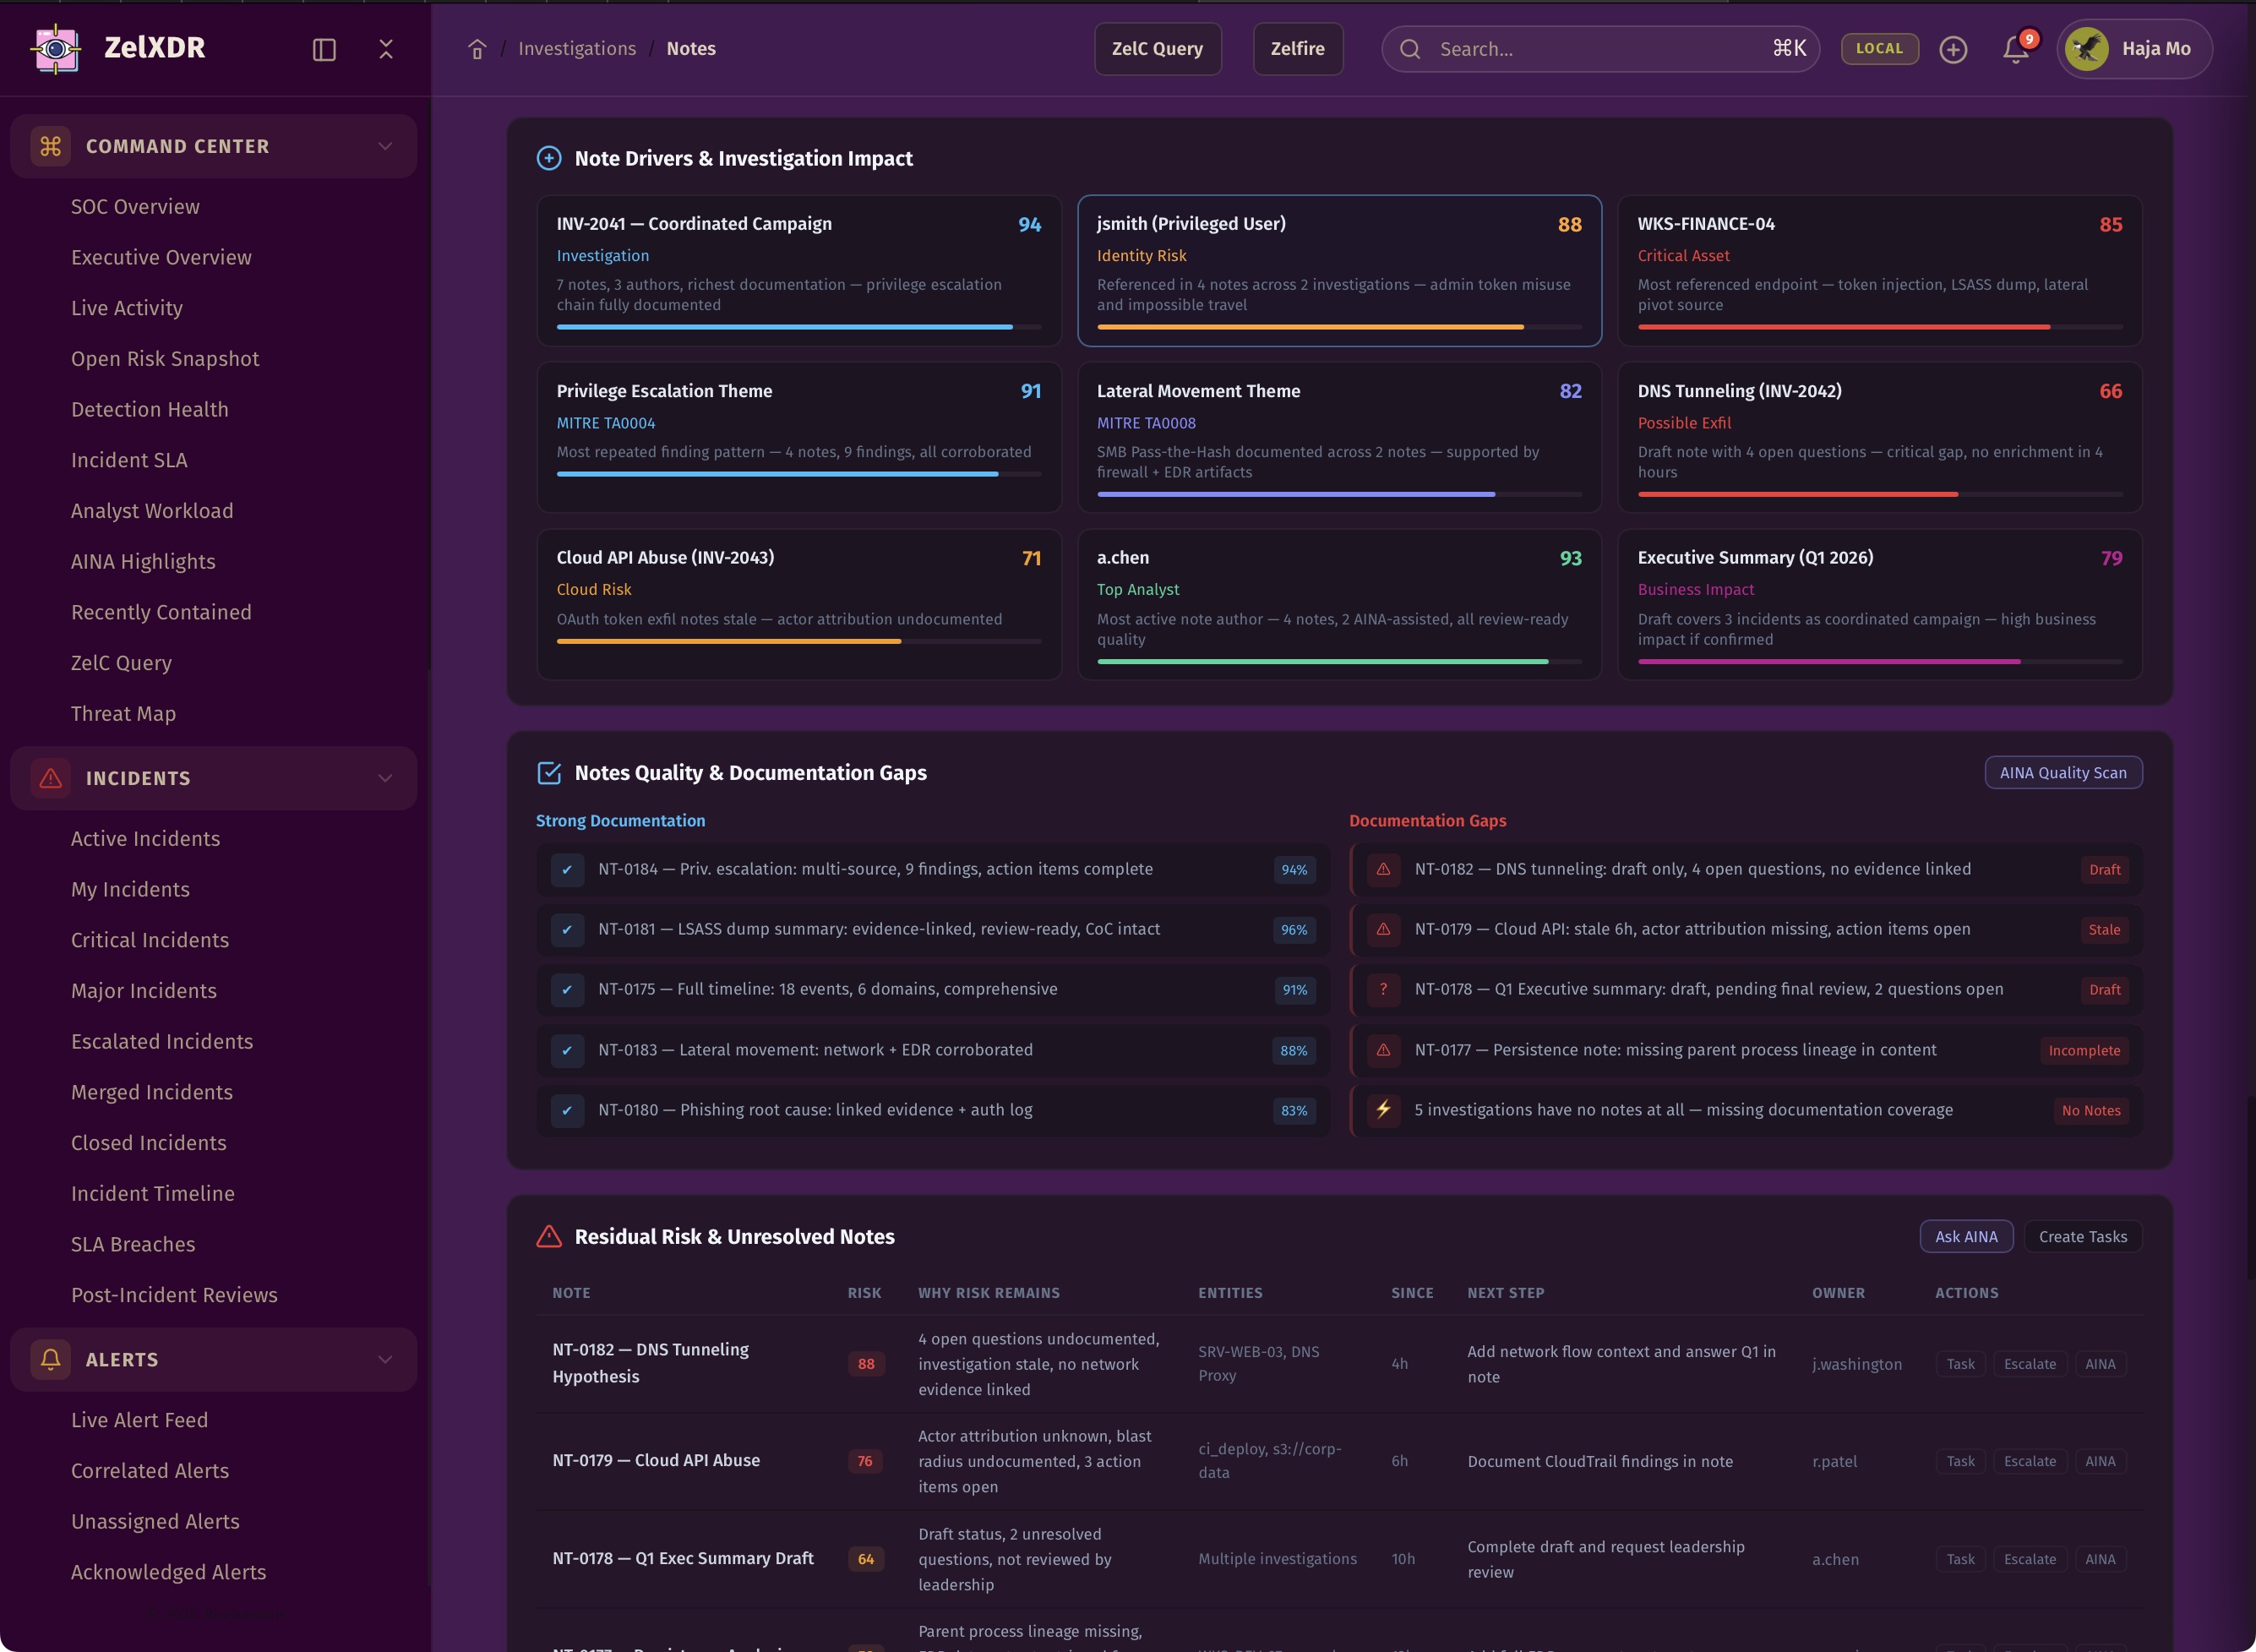
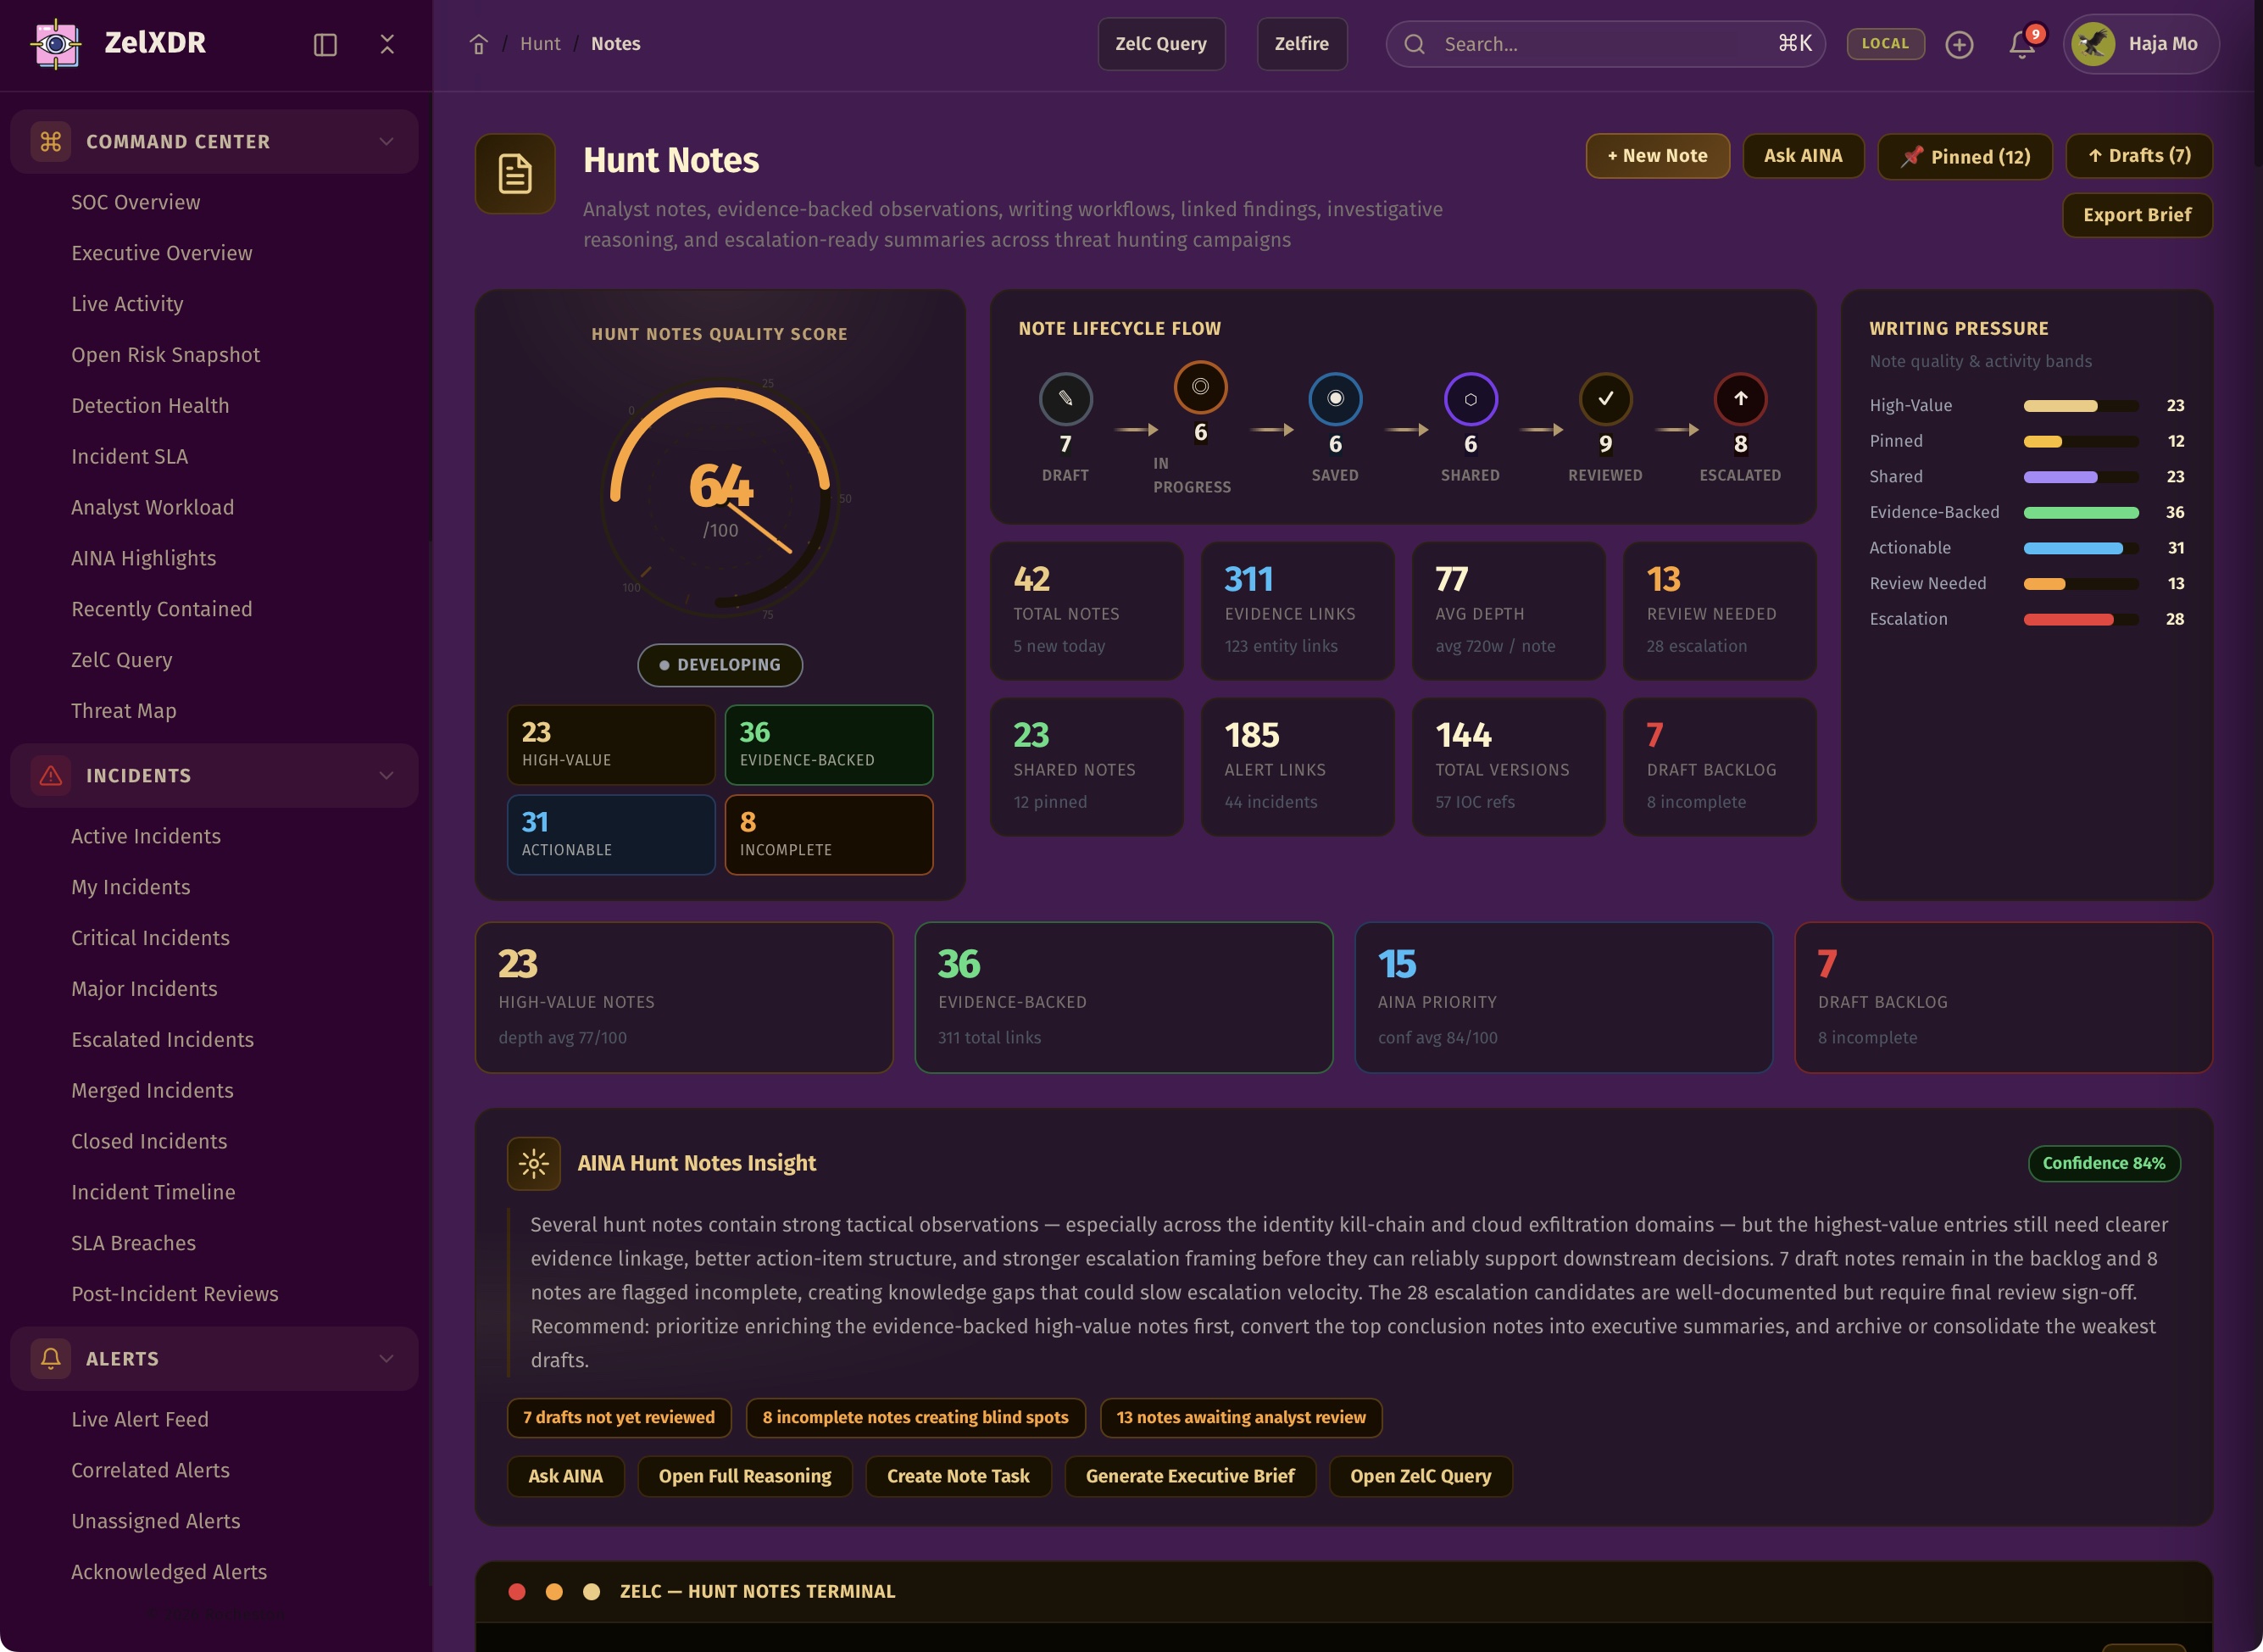
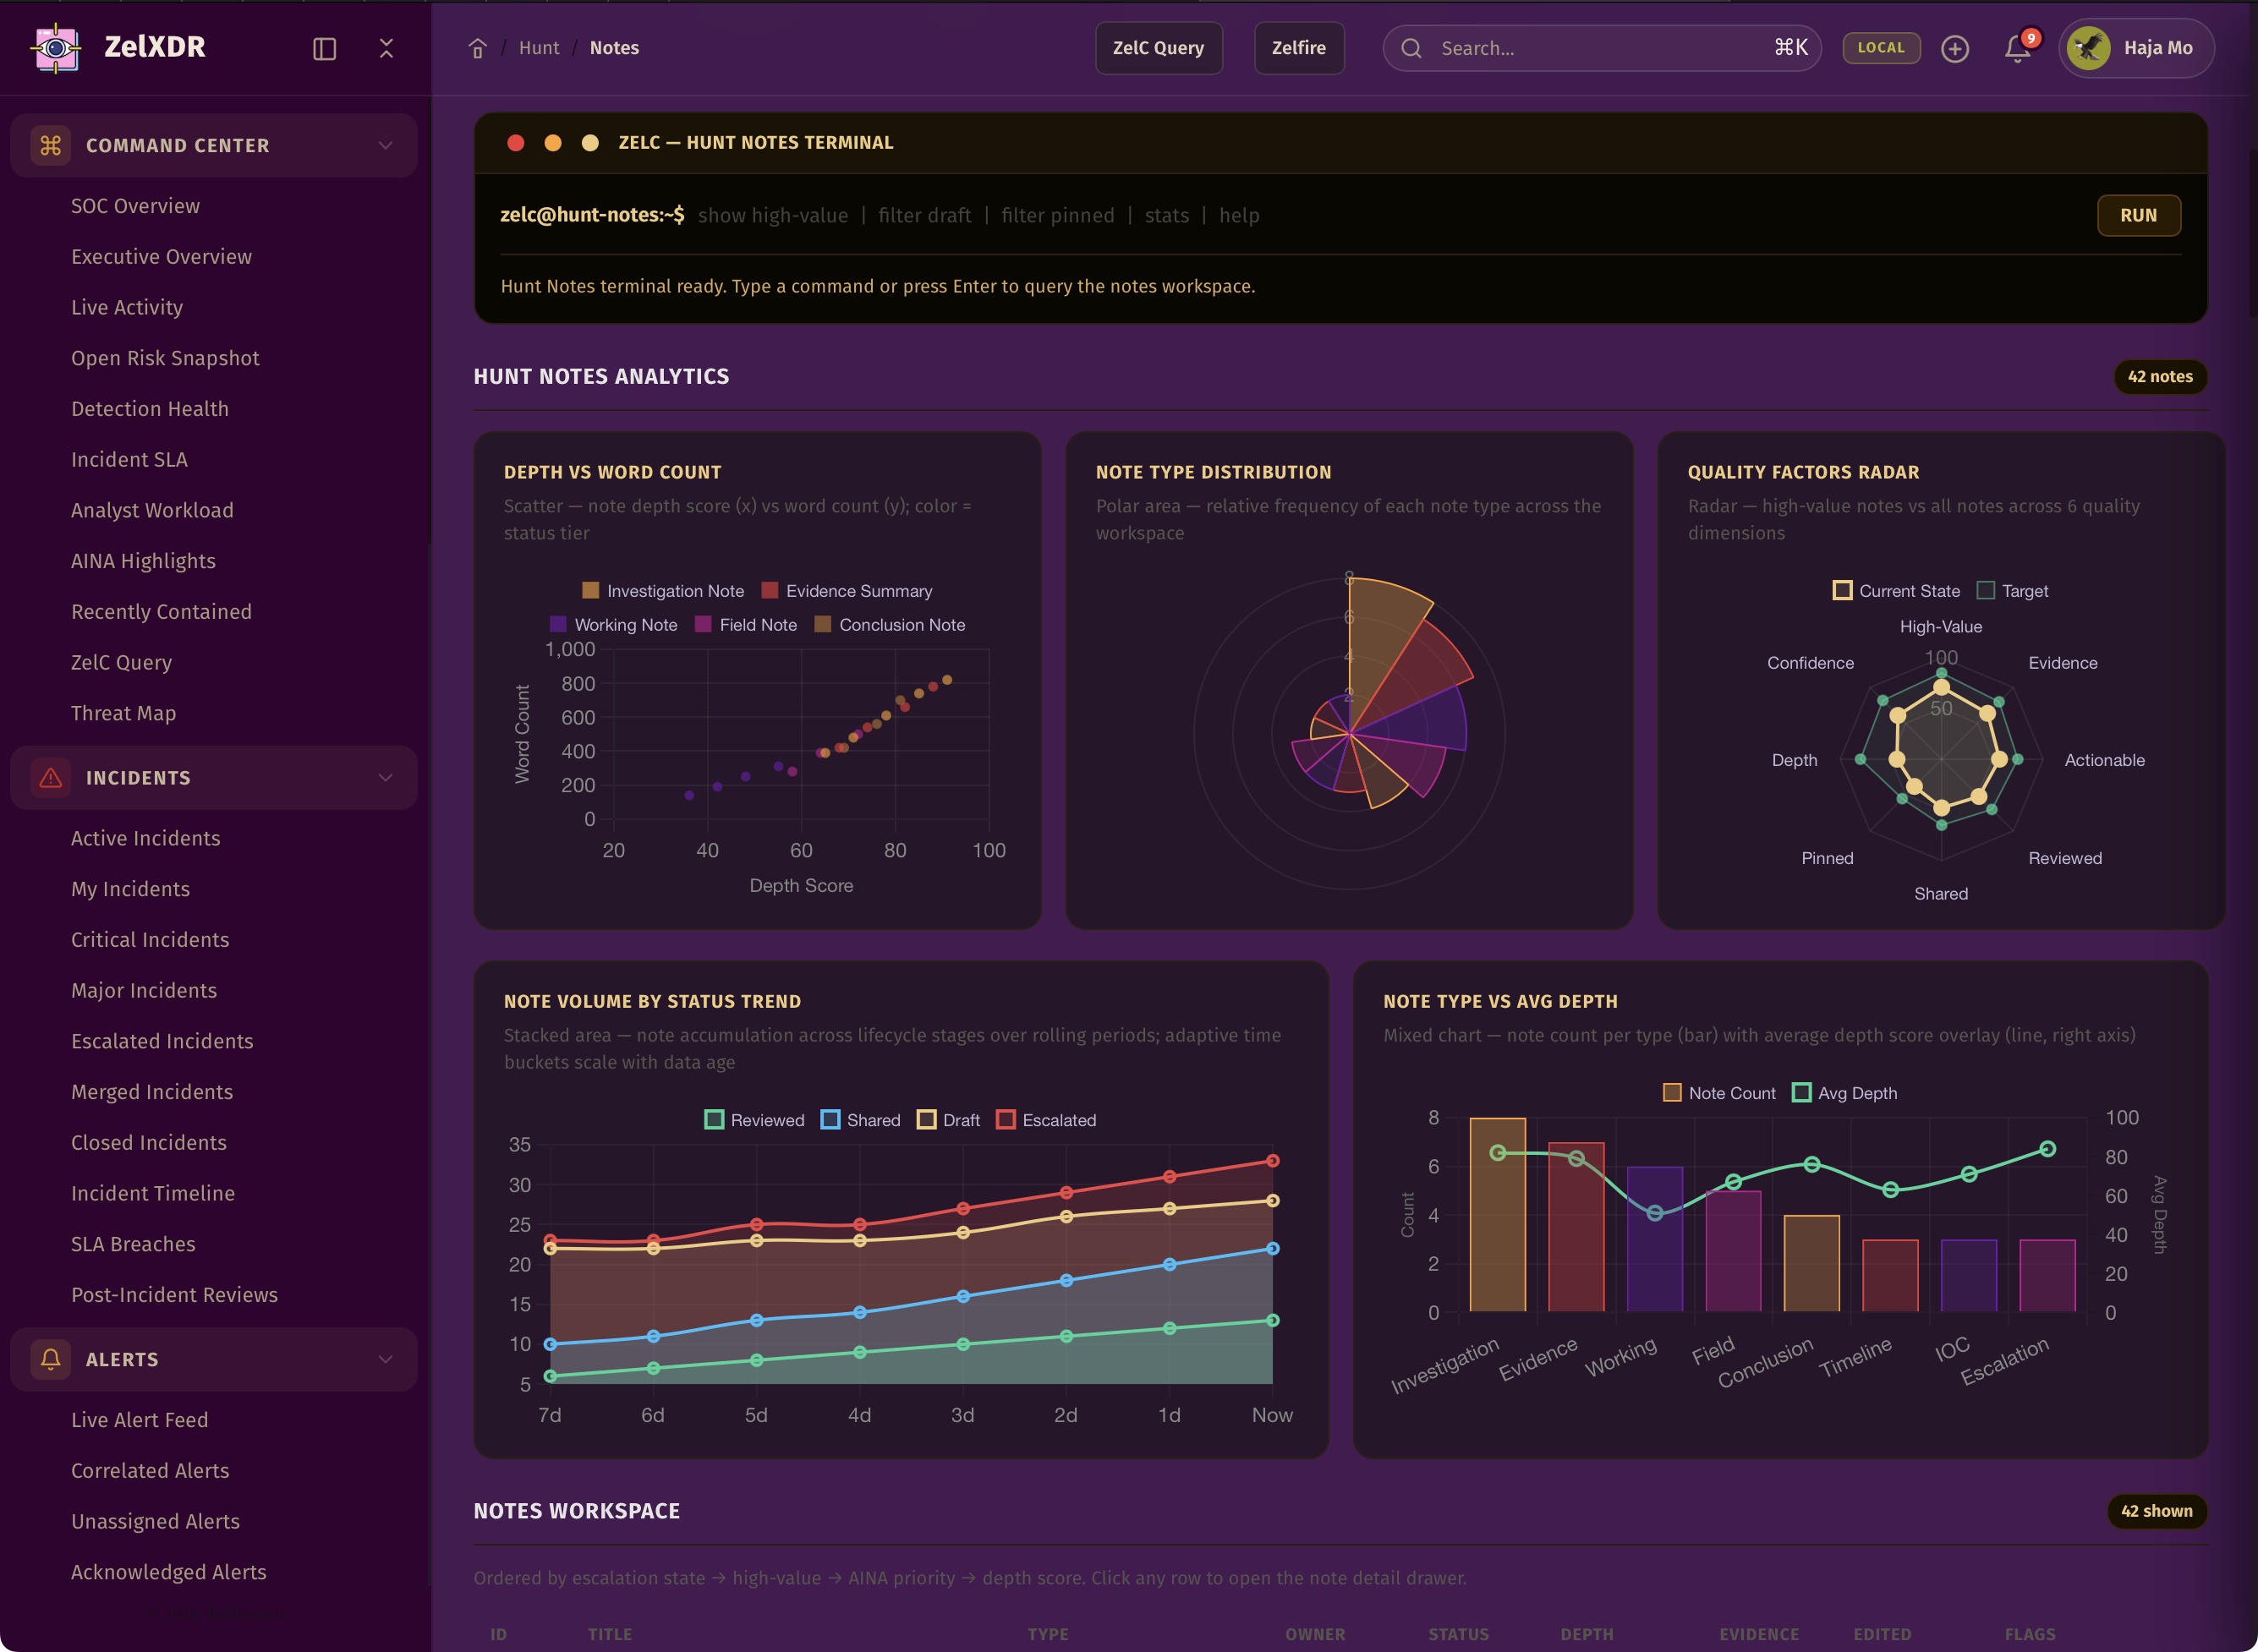
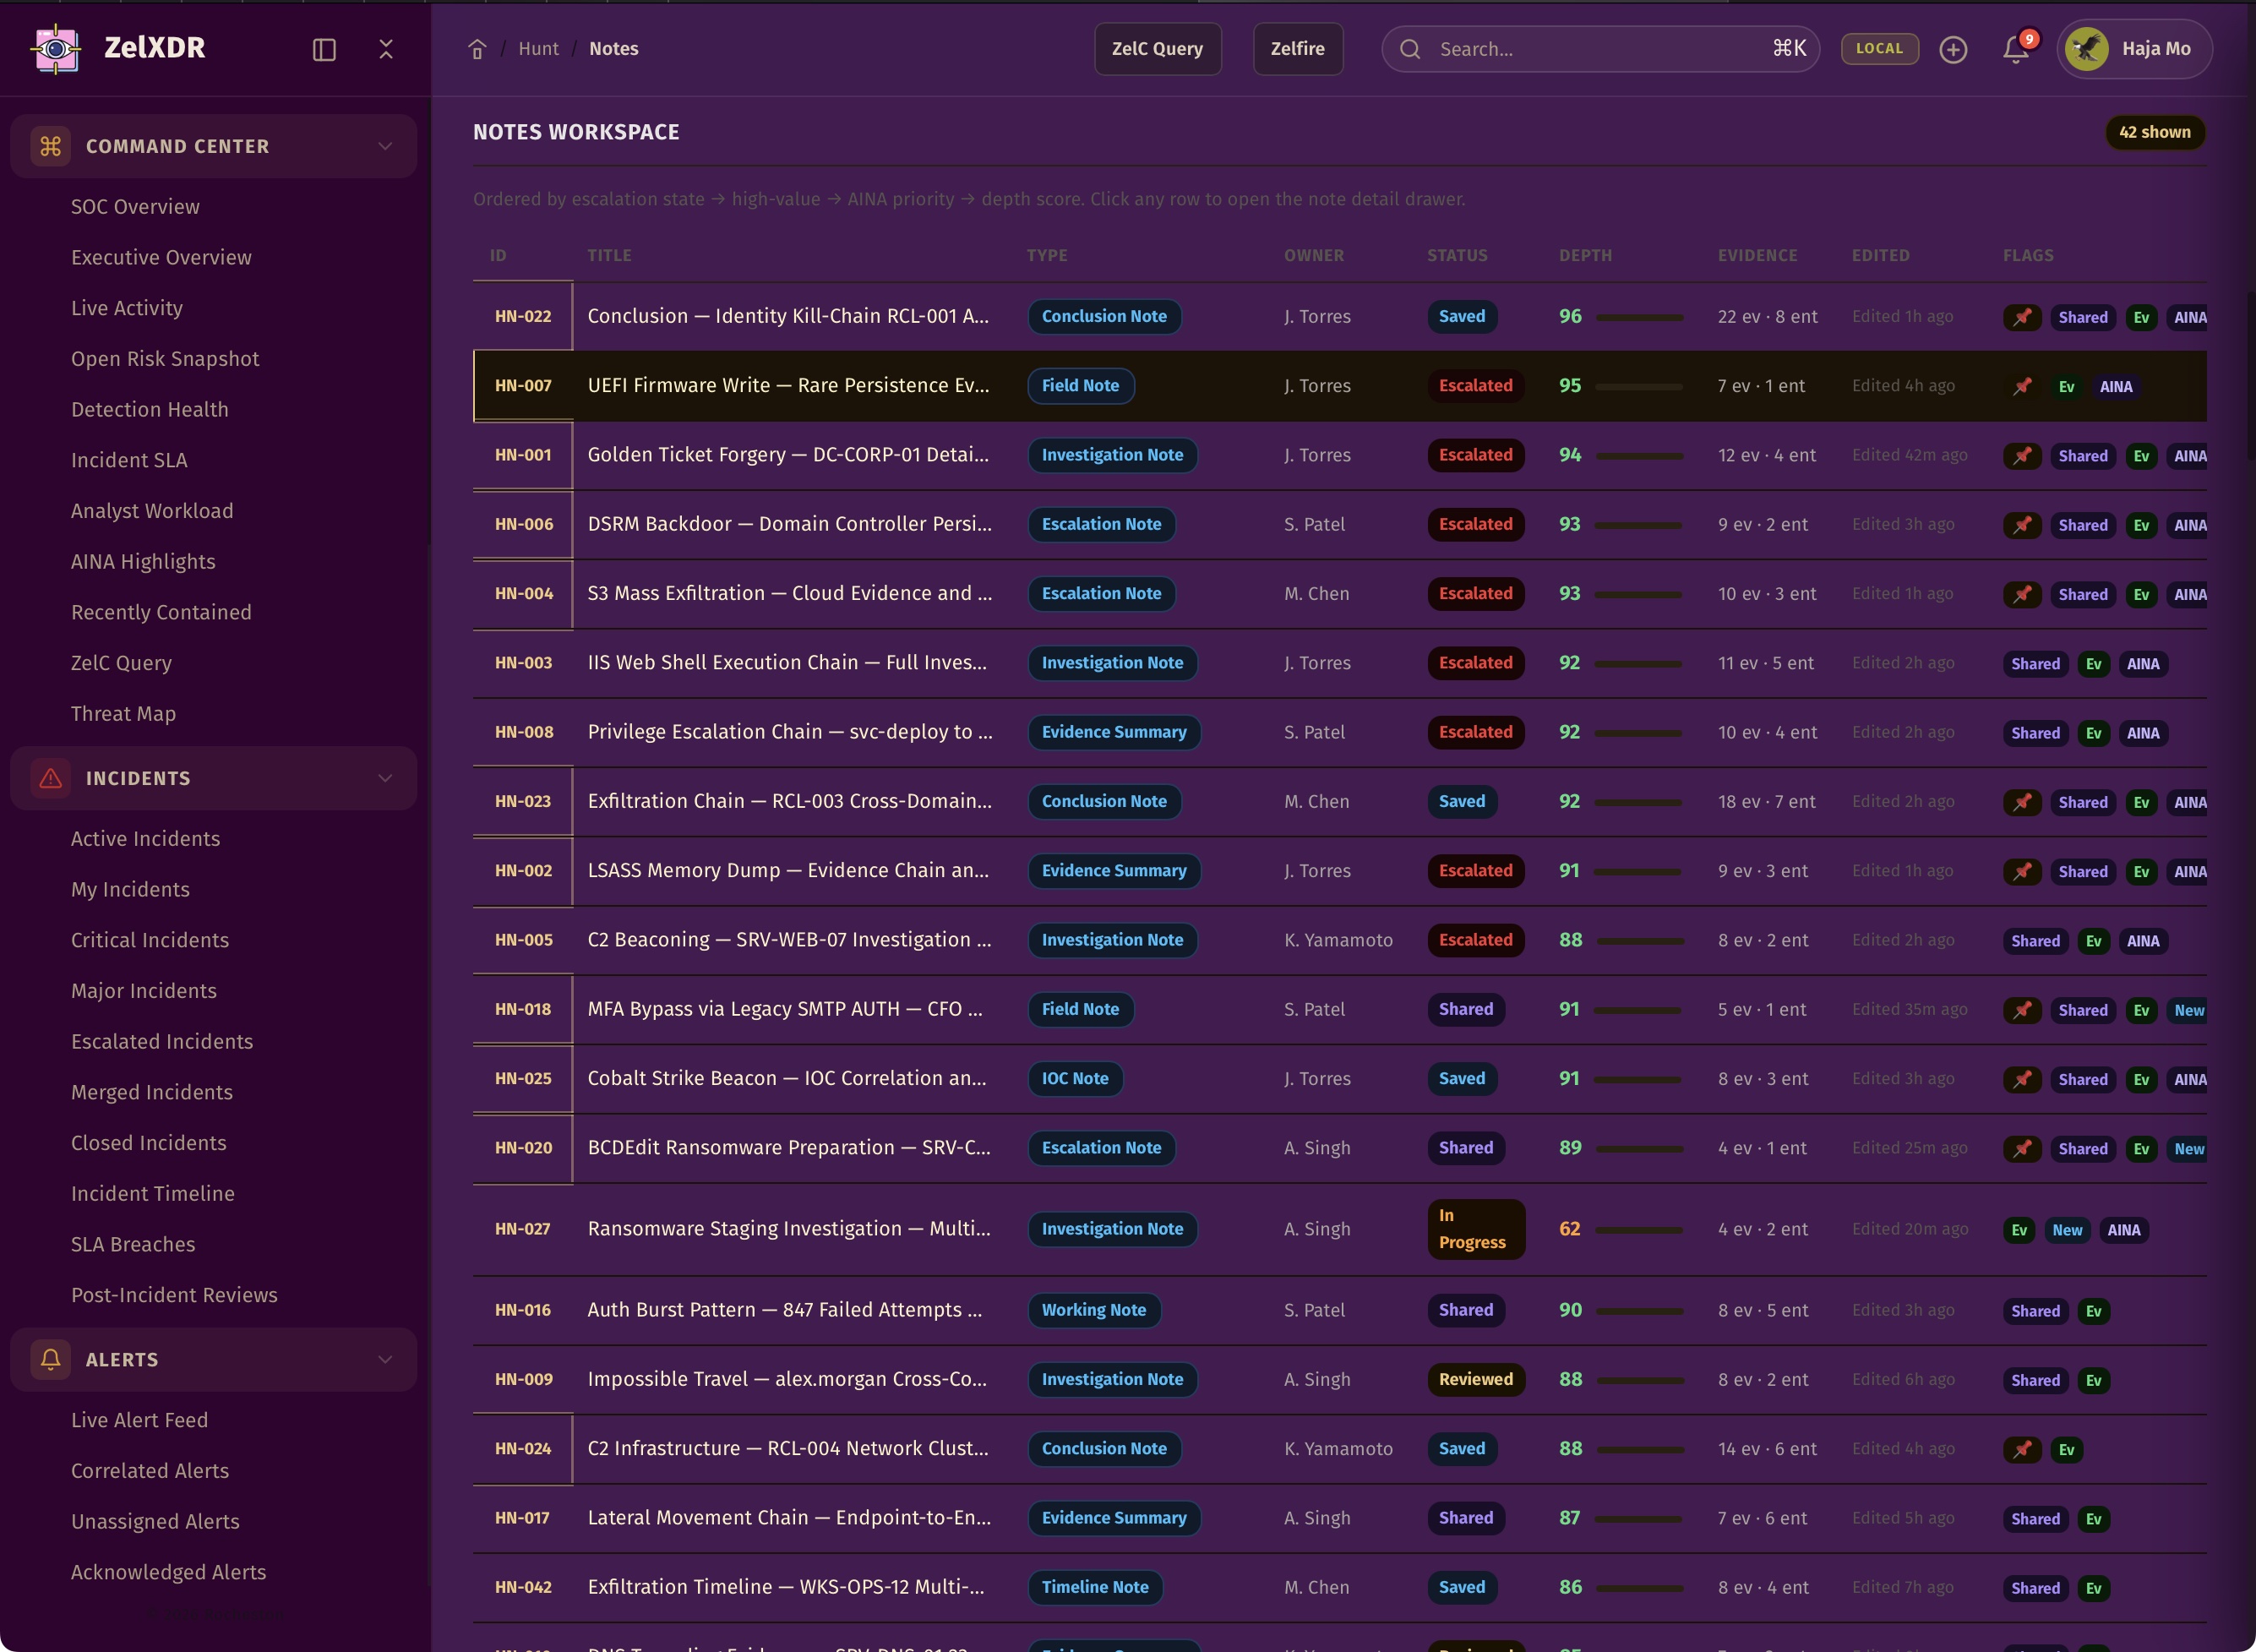
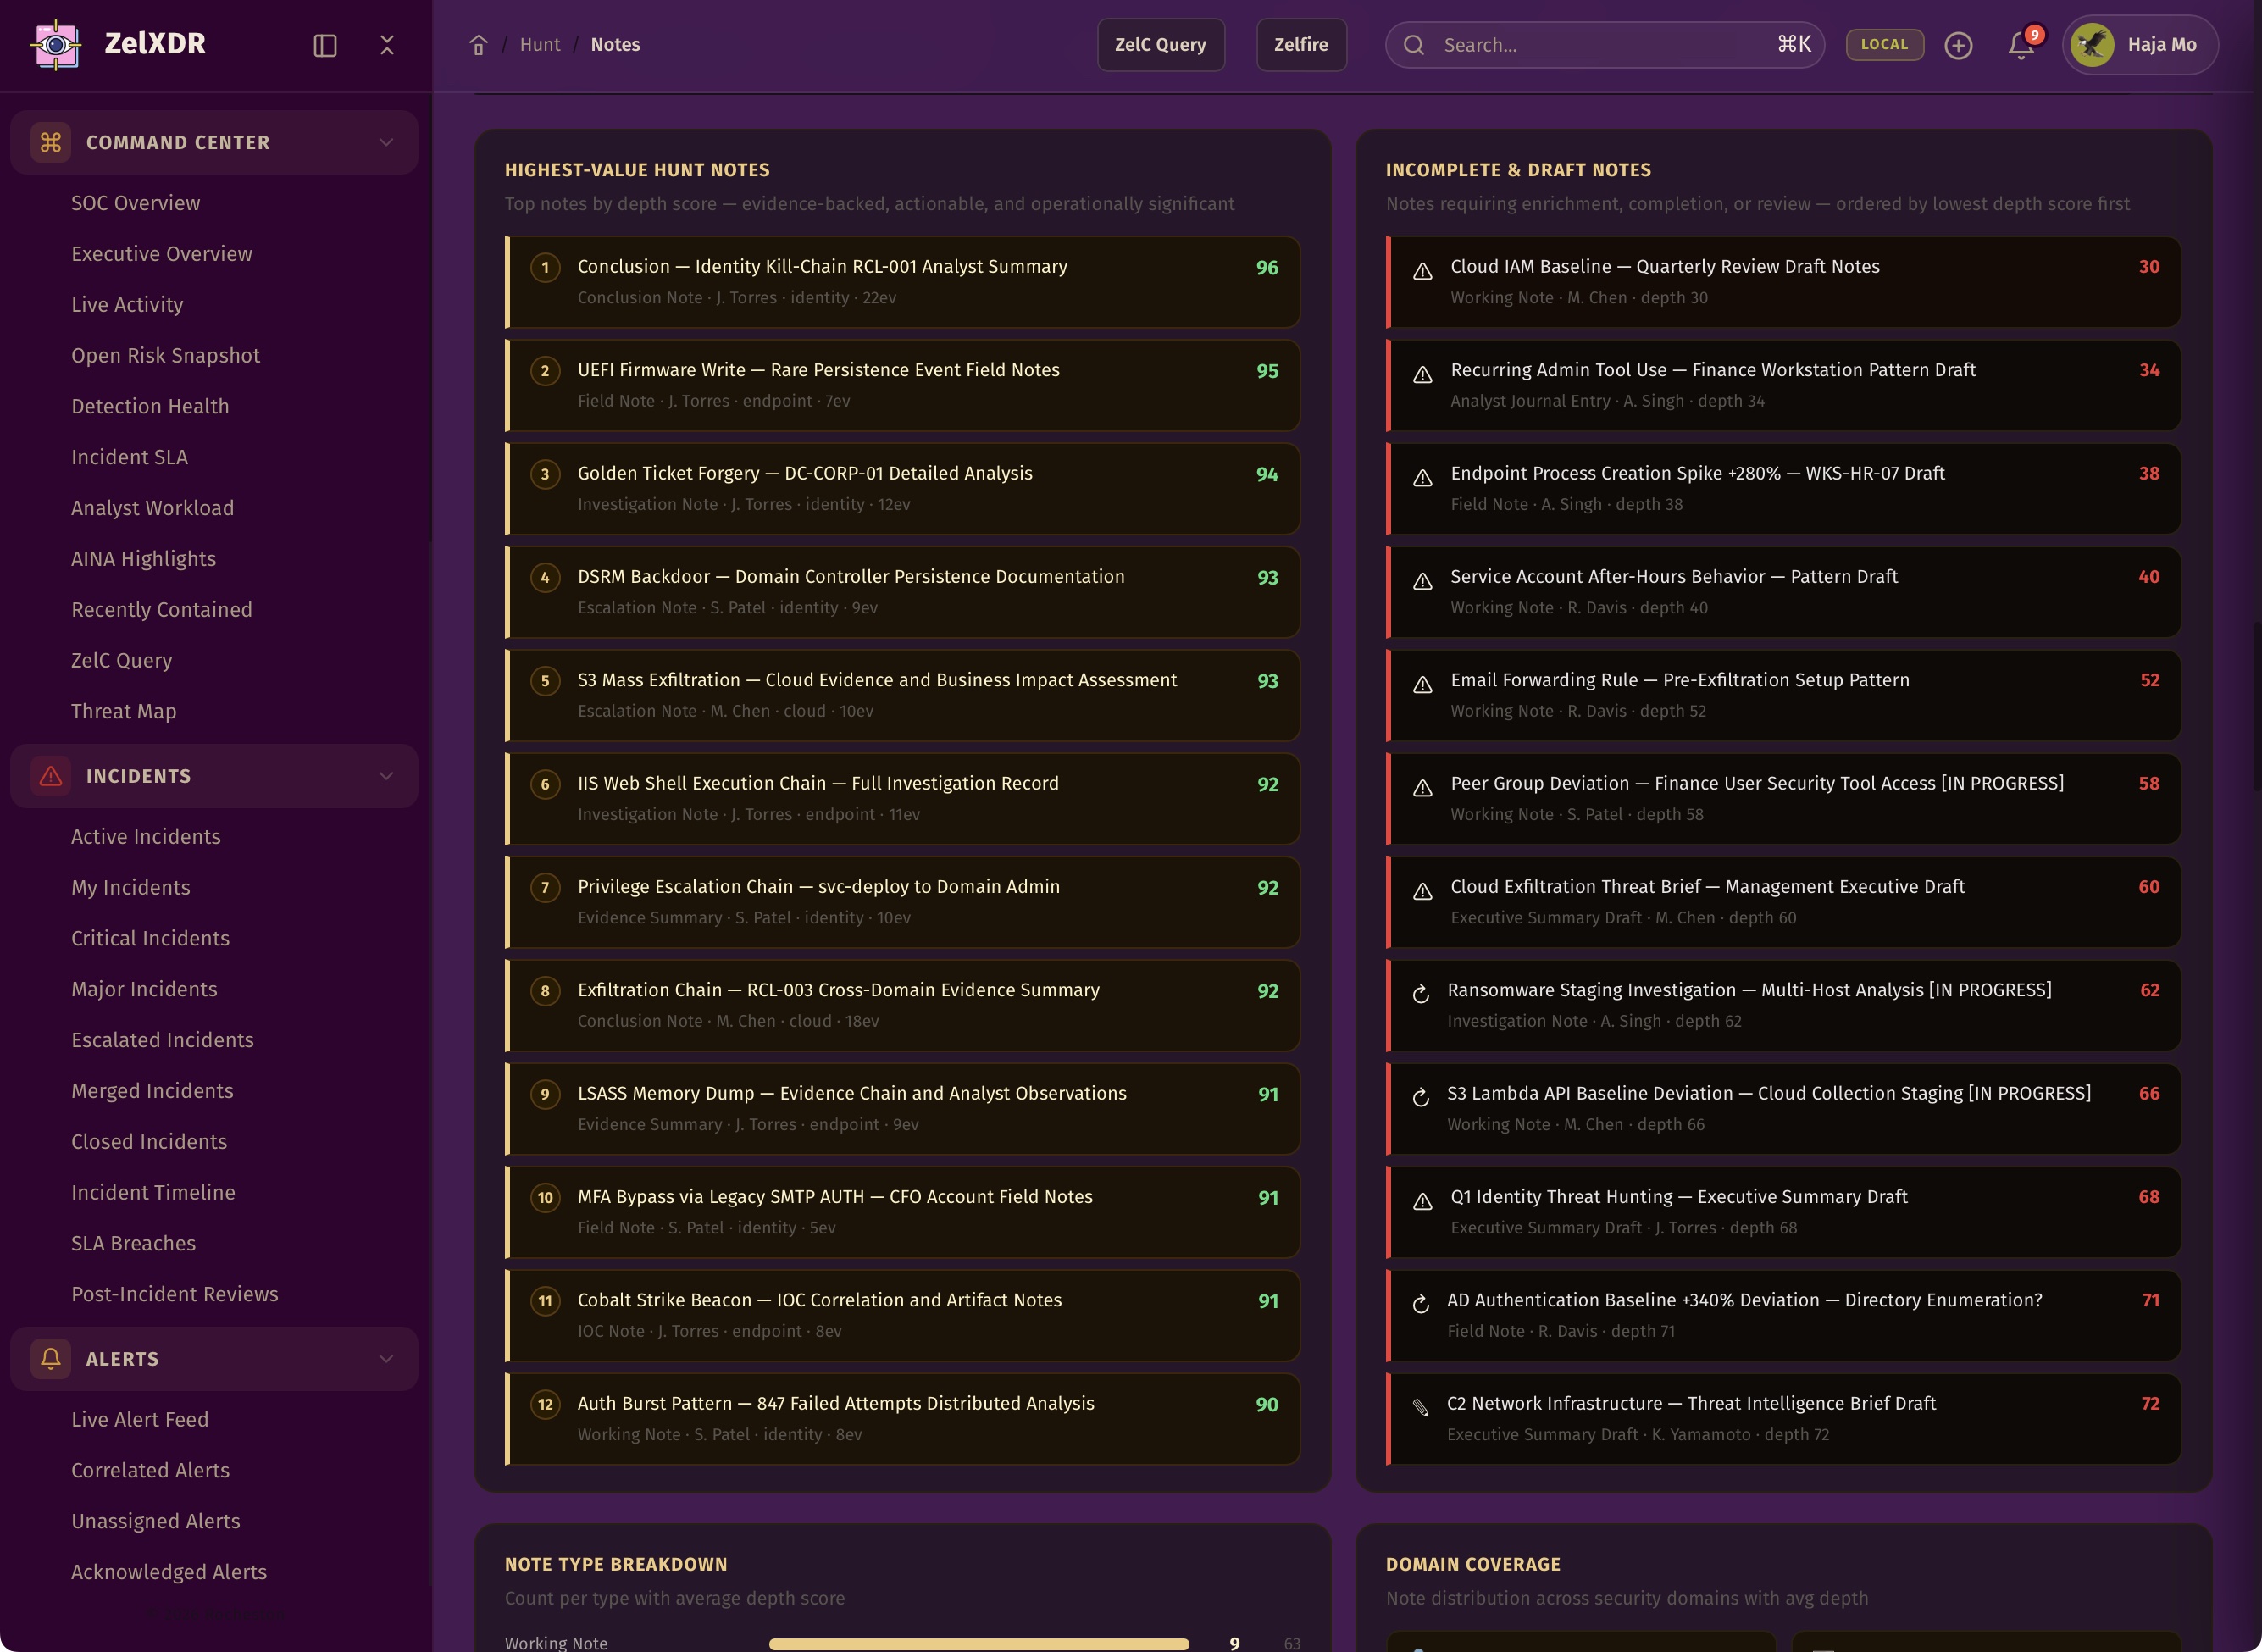
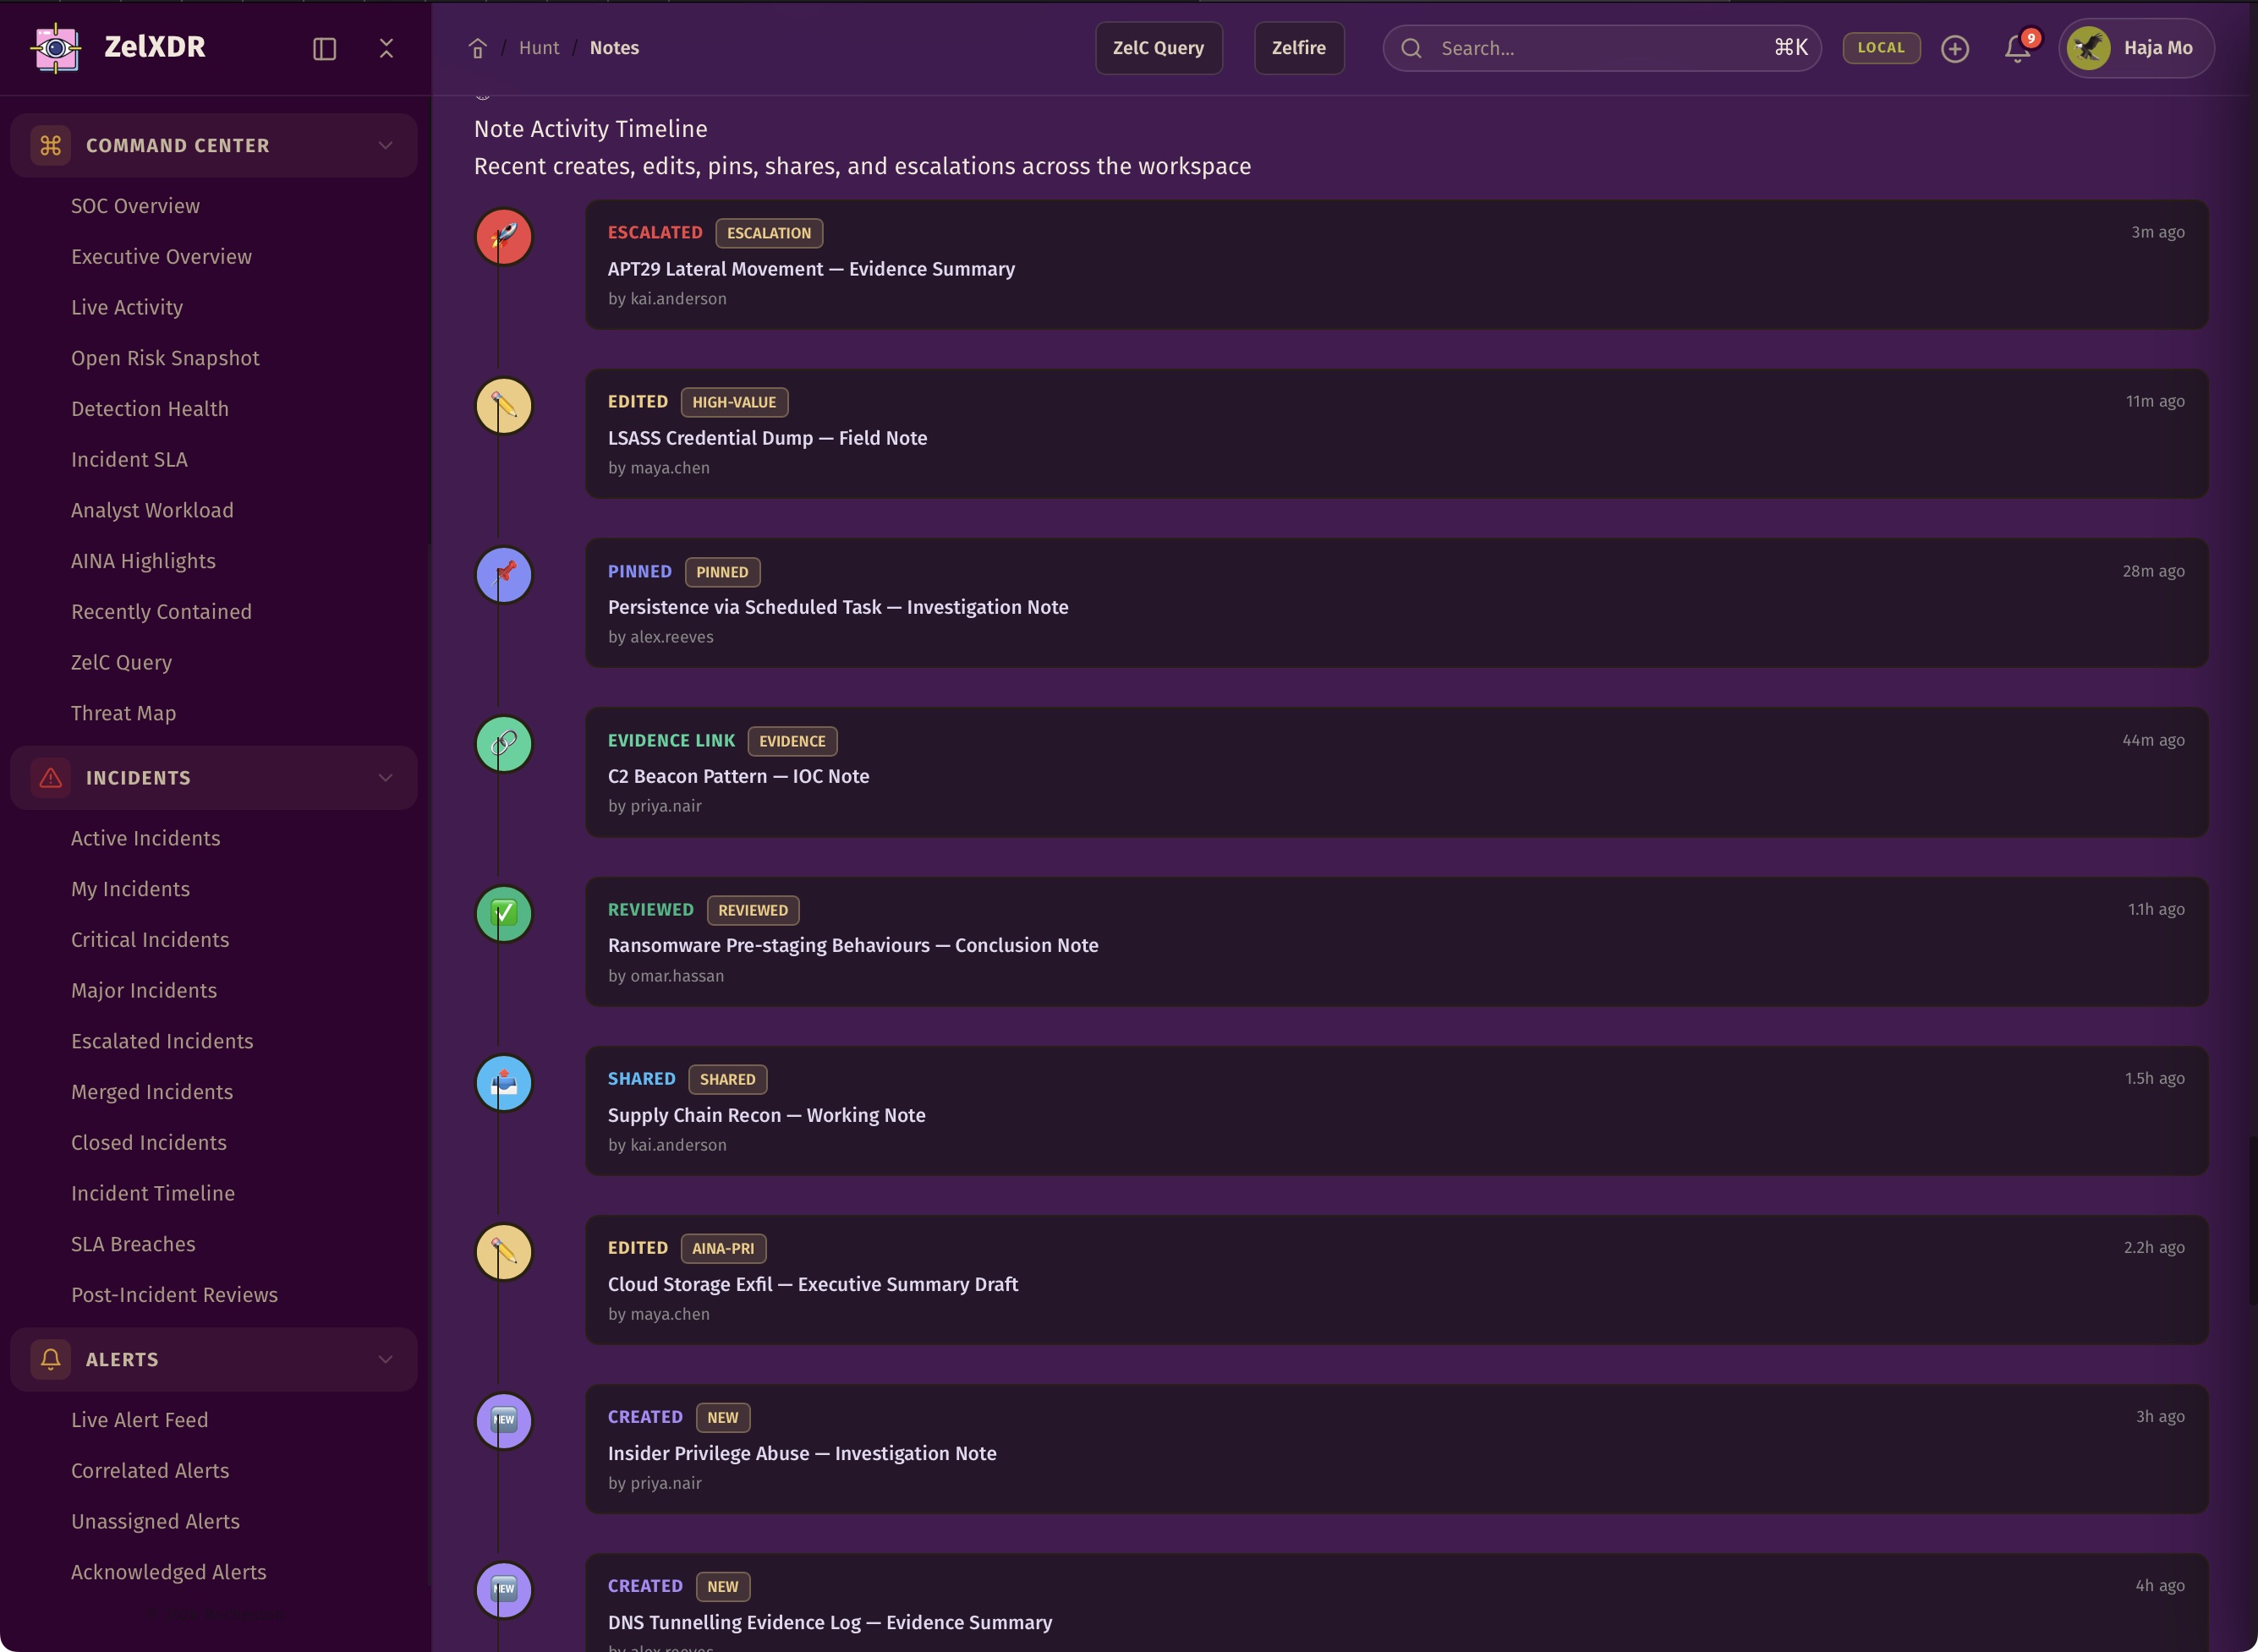
ZelXDR includes rich note-taking, evidence linking, drafting, editing, sharing, pinning, and AI-assisted writing so investigation knowledge is preserved, usable, and operationally valuable.
Good notes are operational assets, not personal scraps.
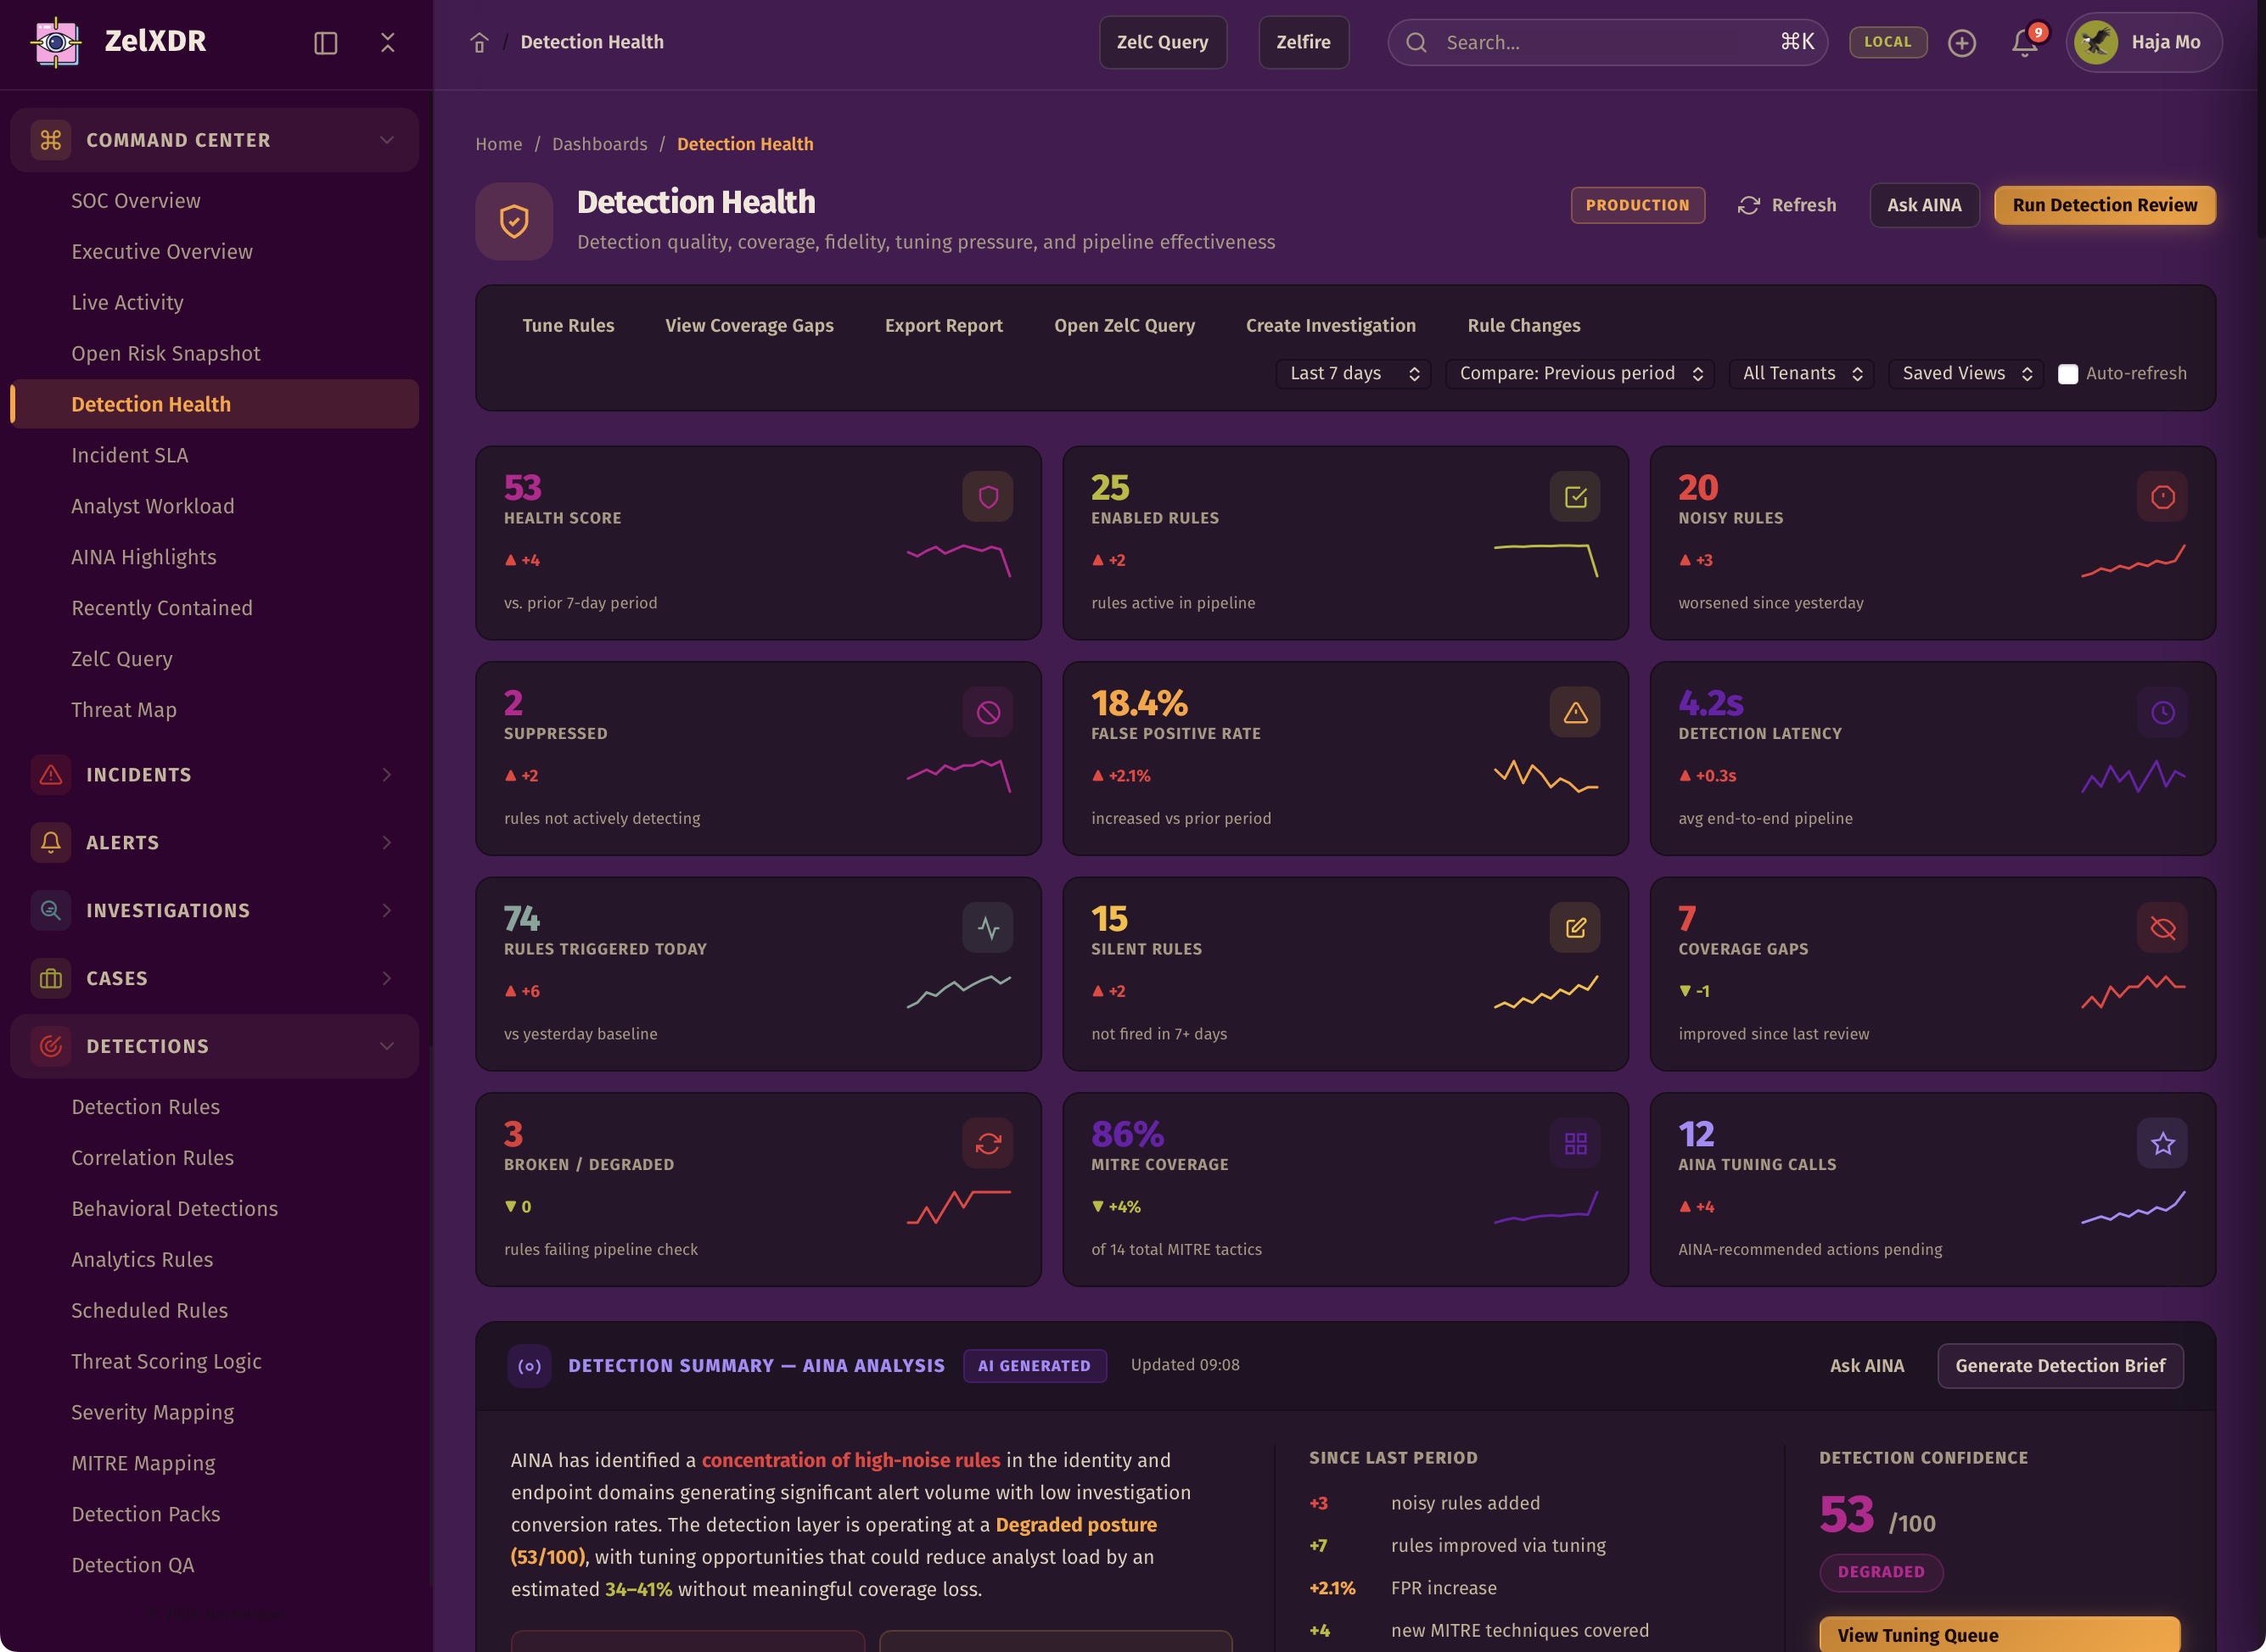
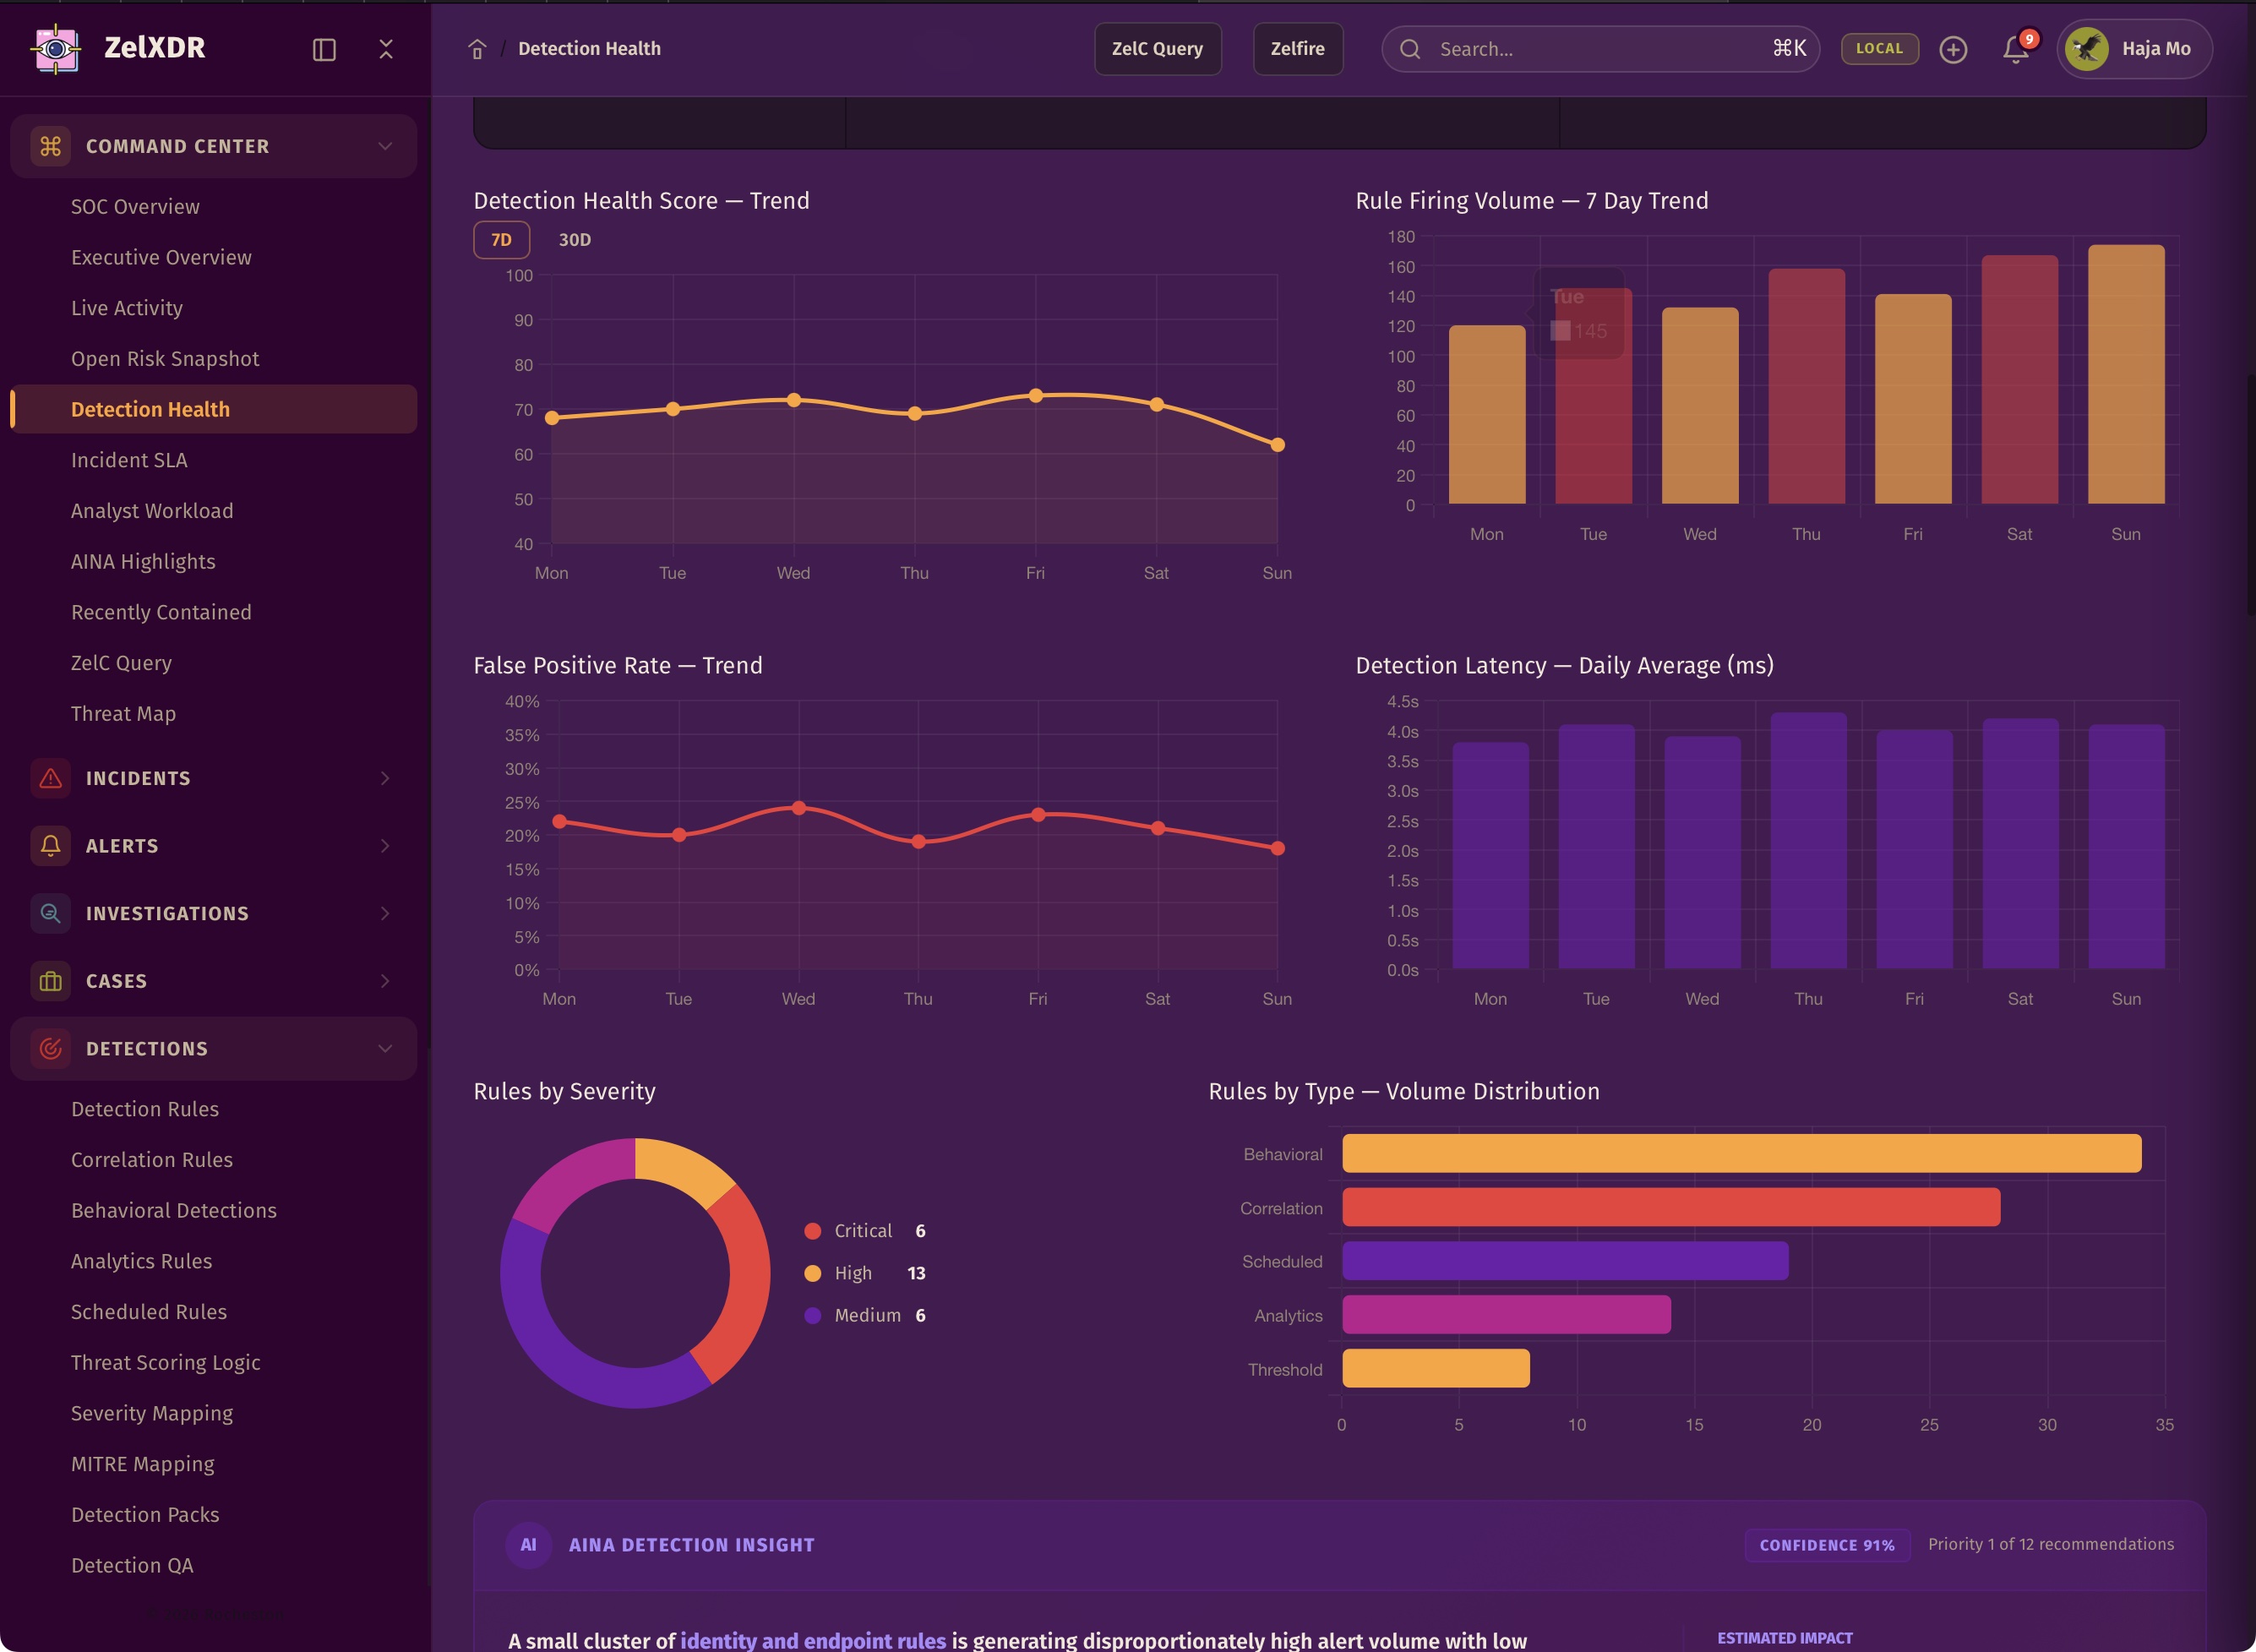
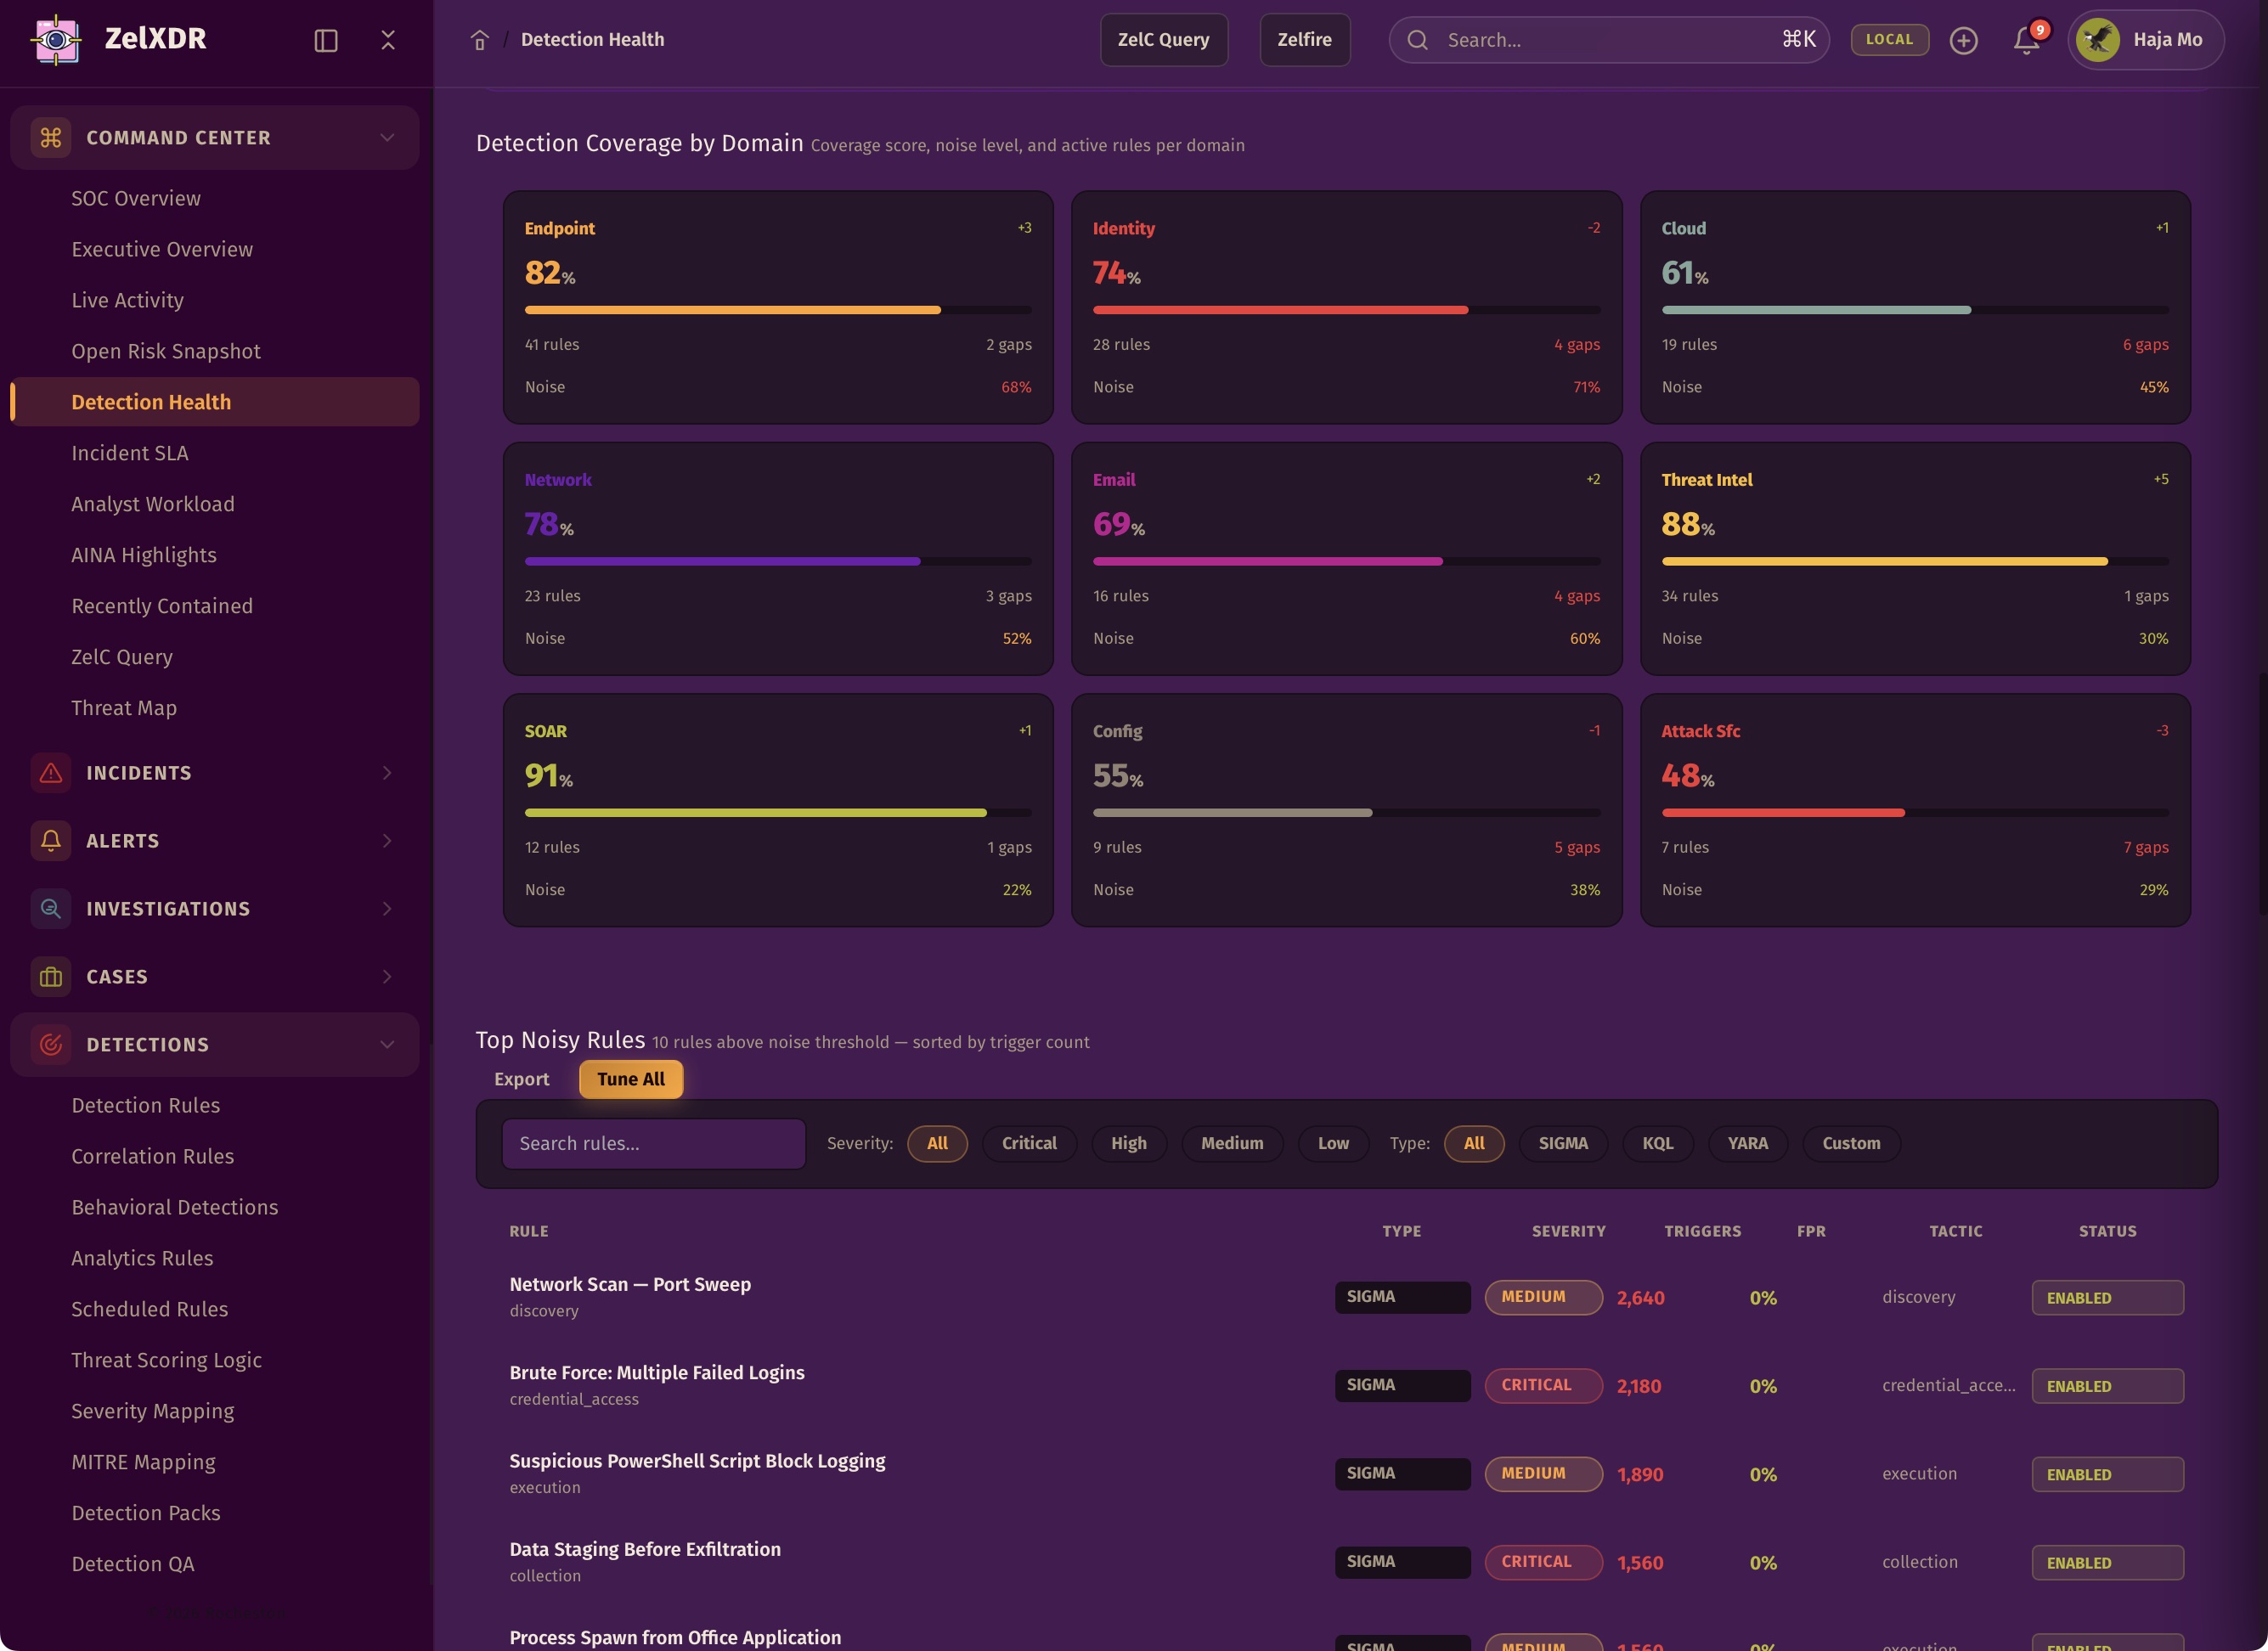
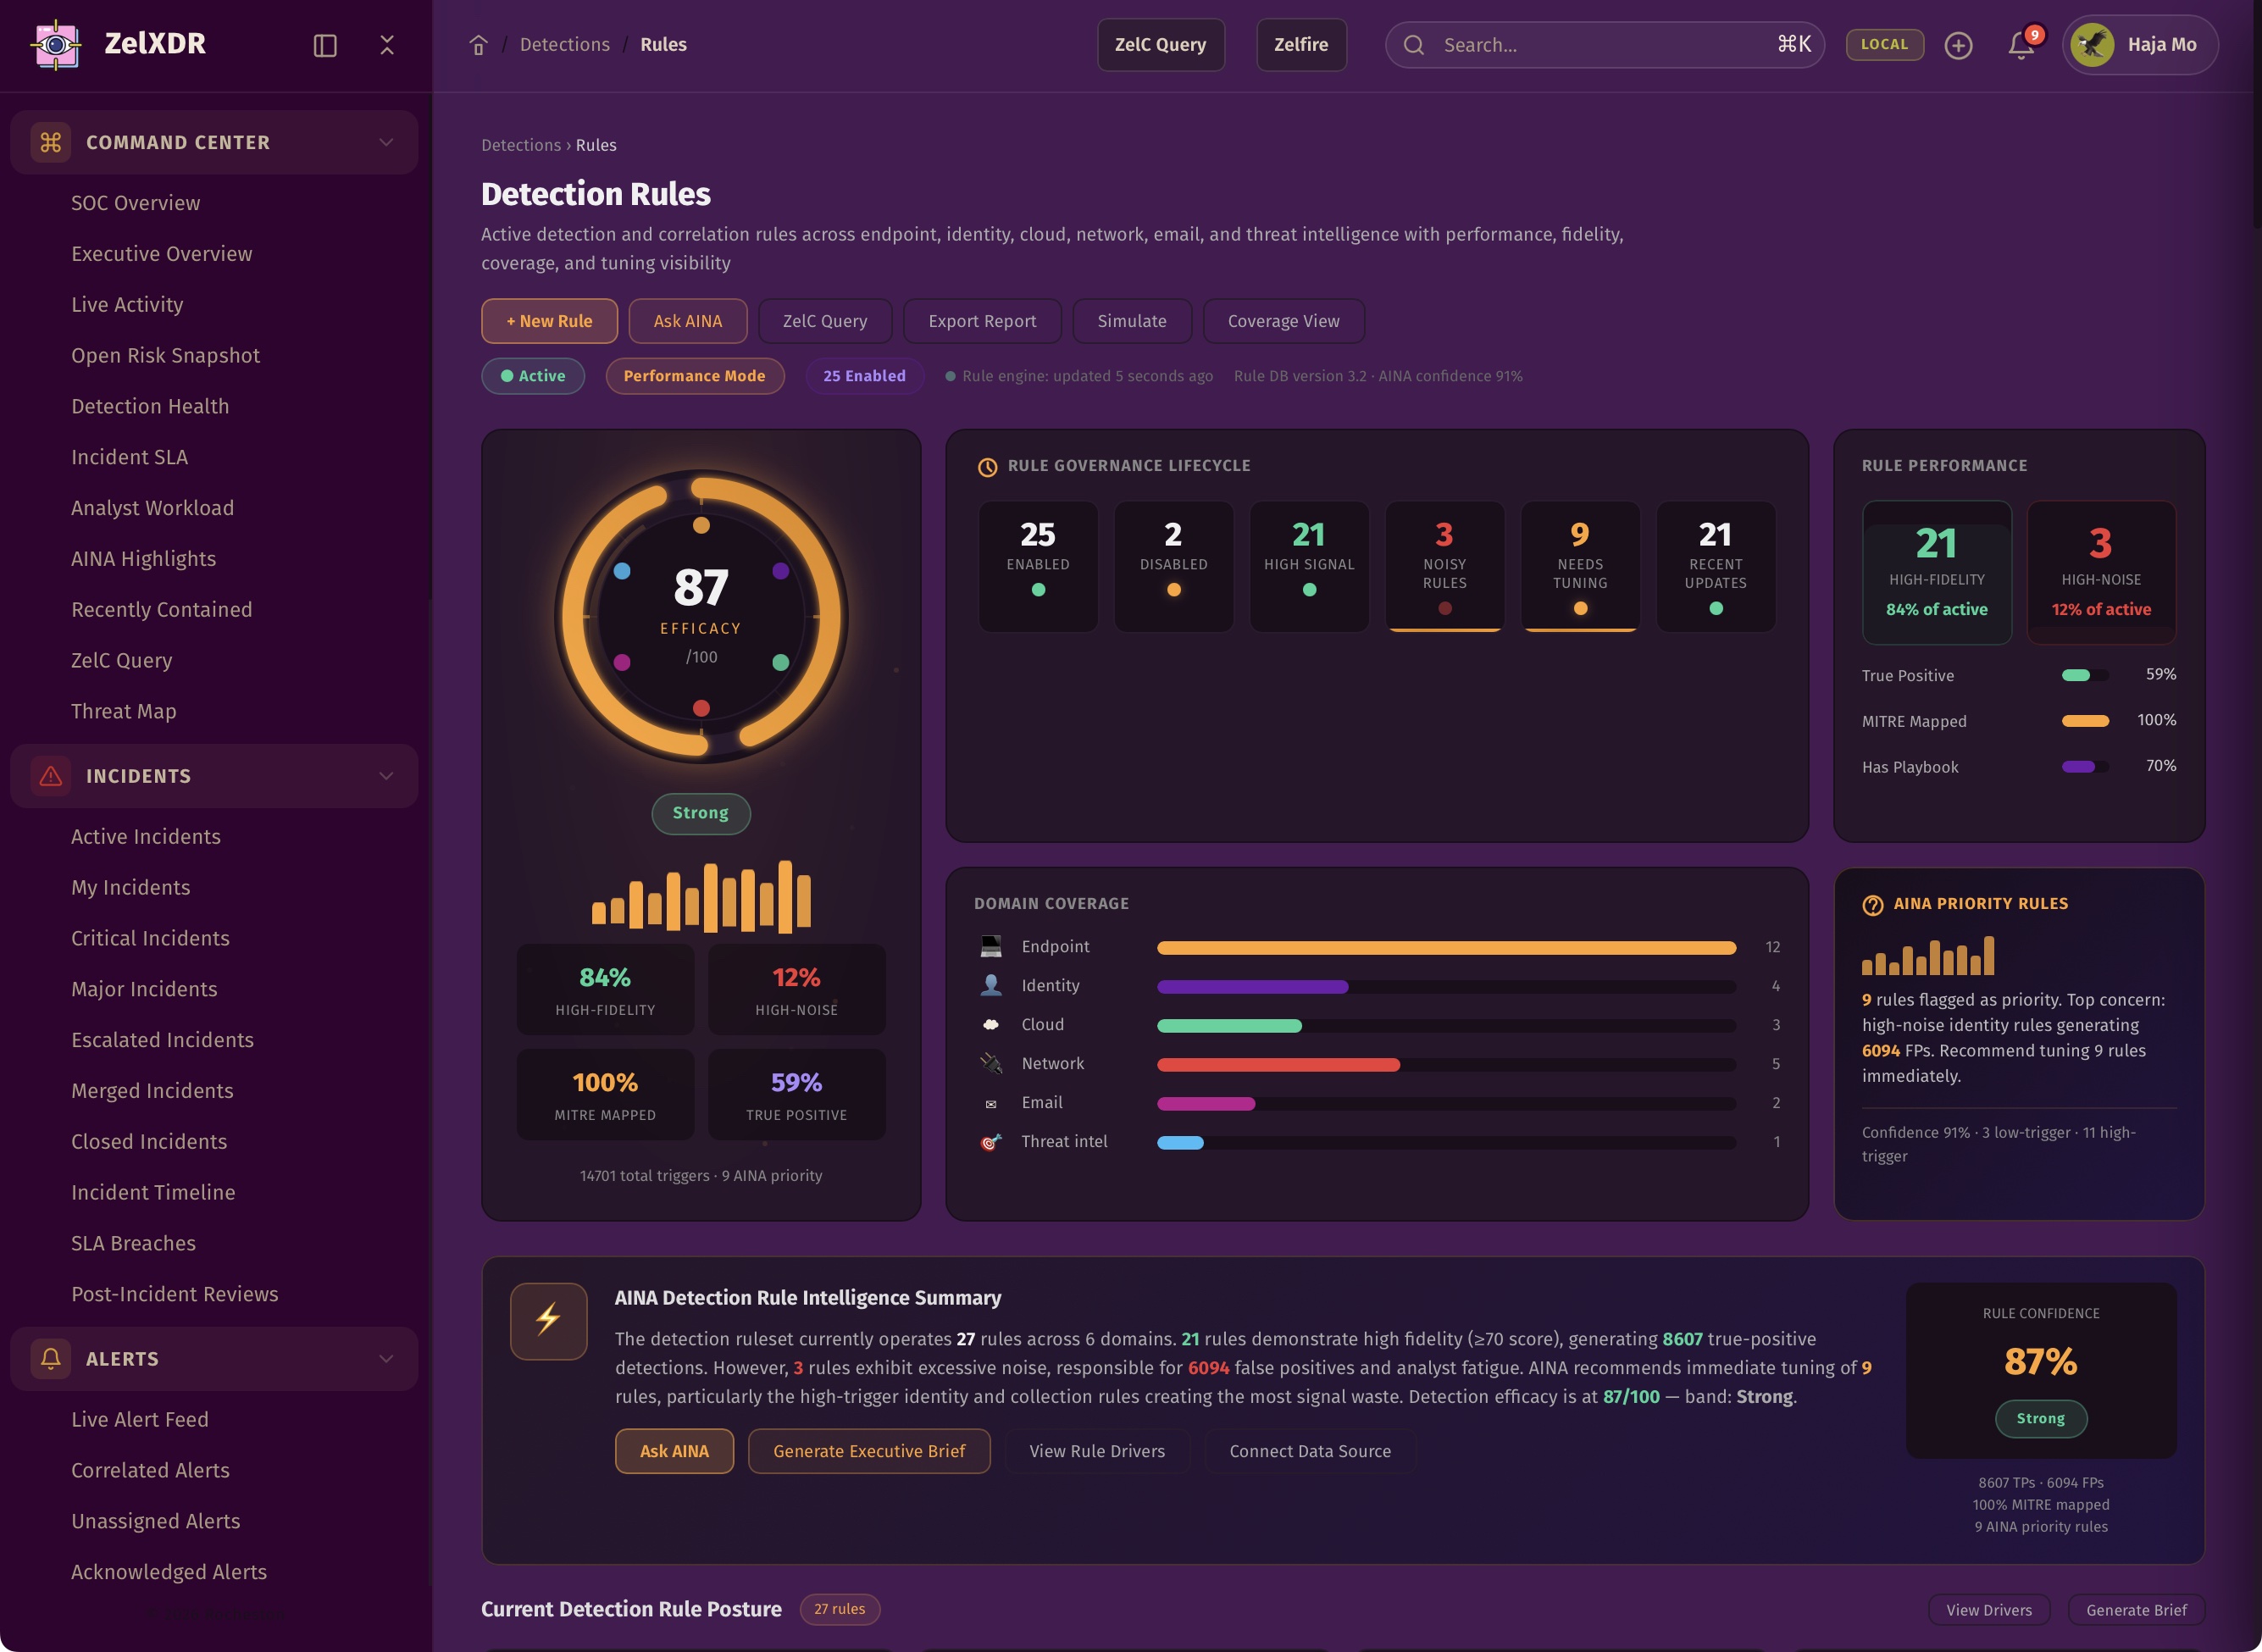
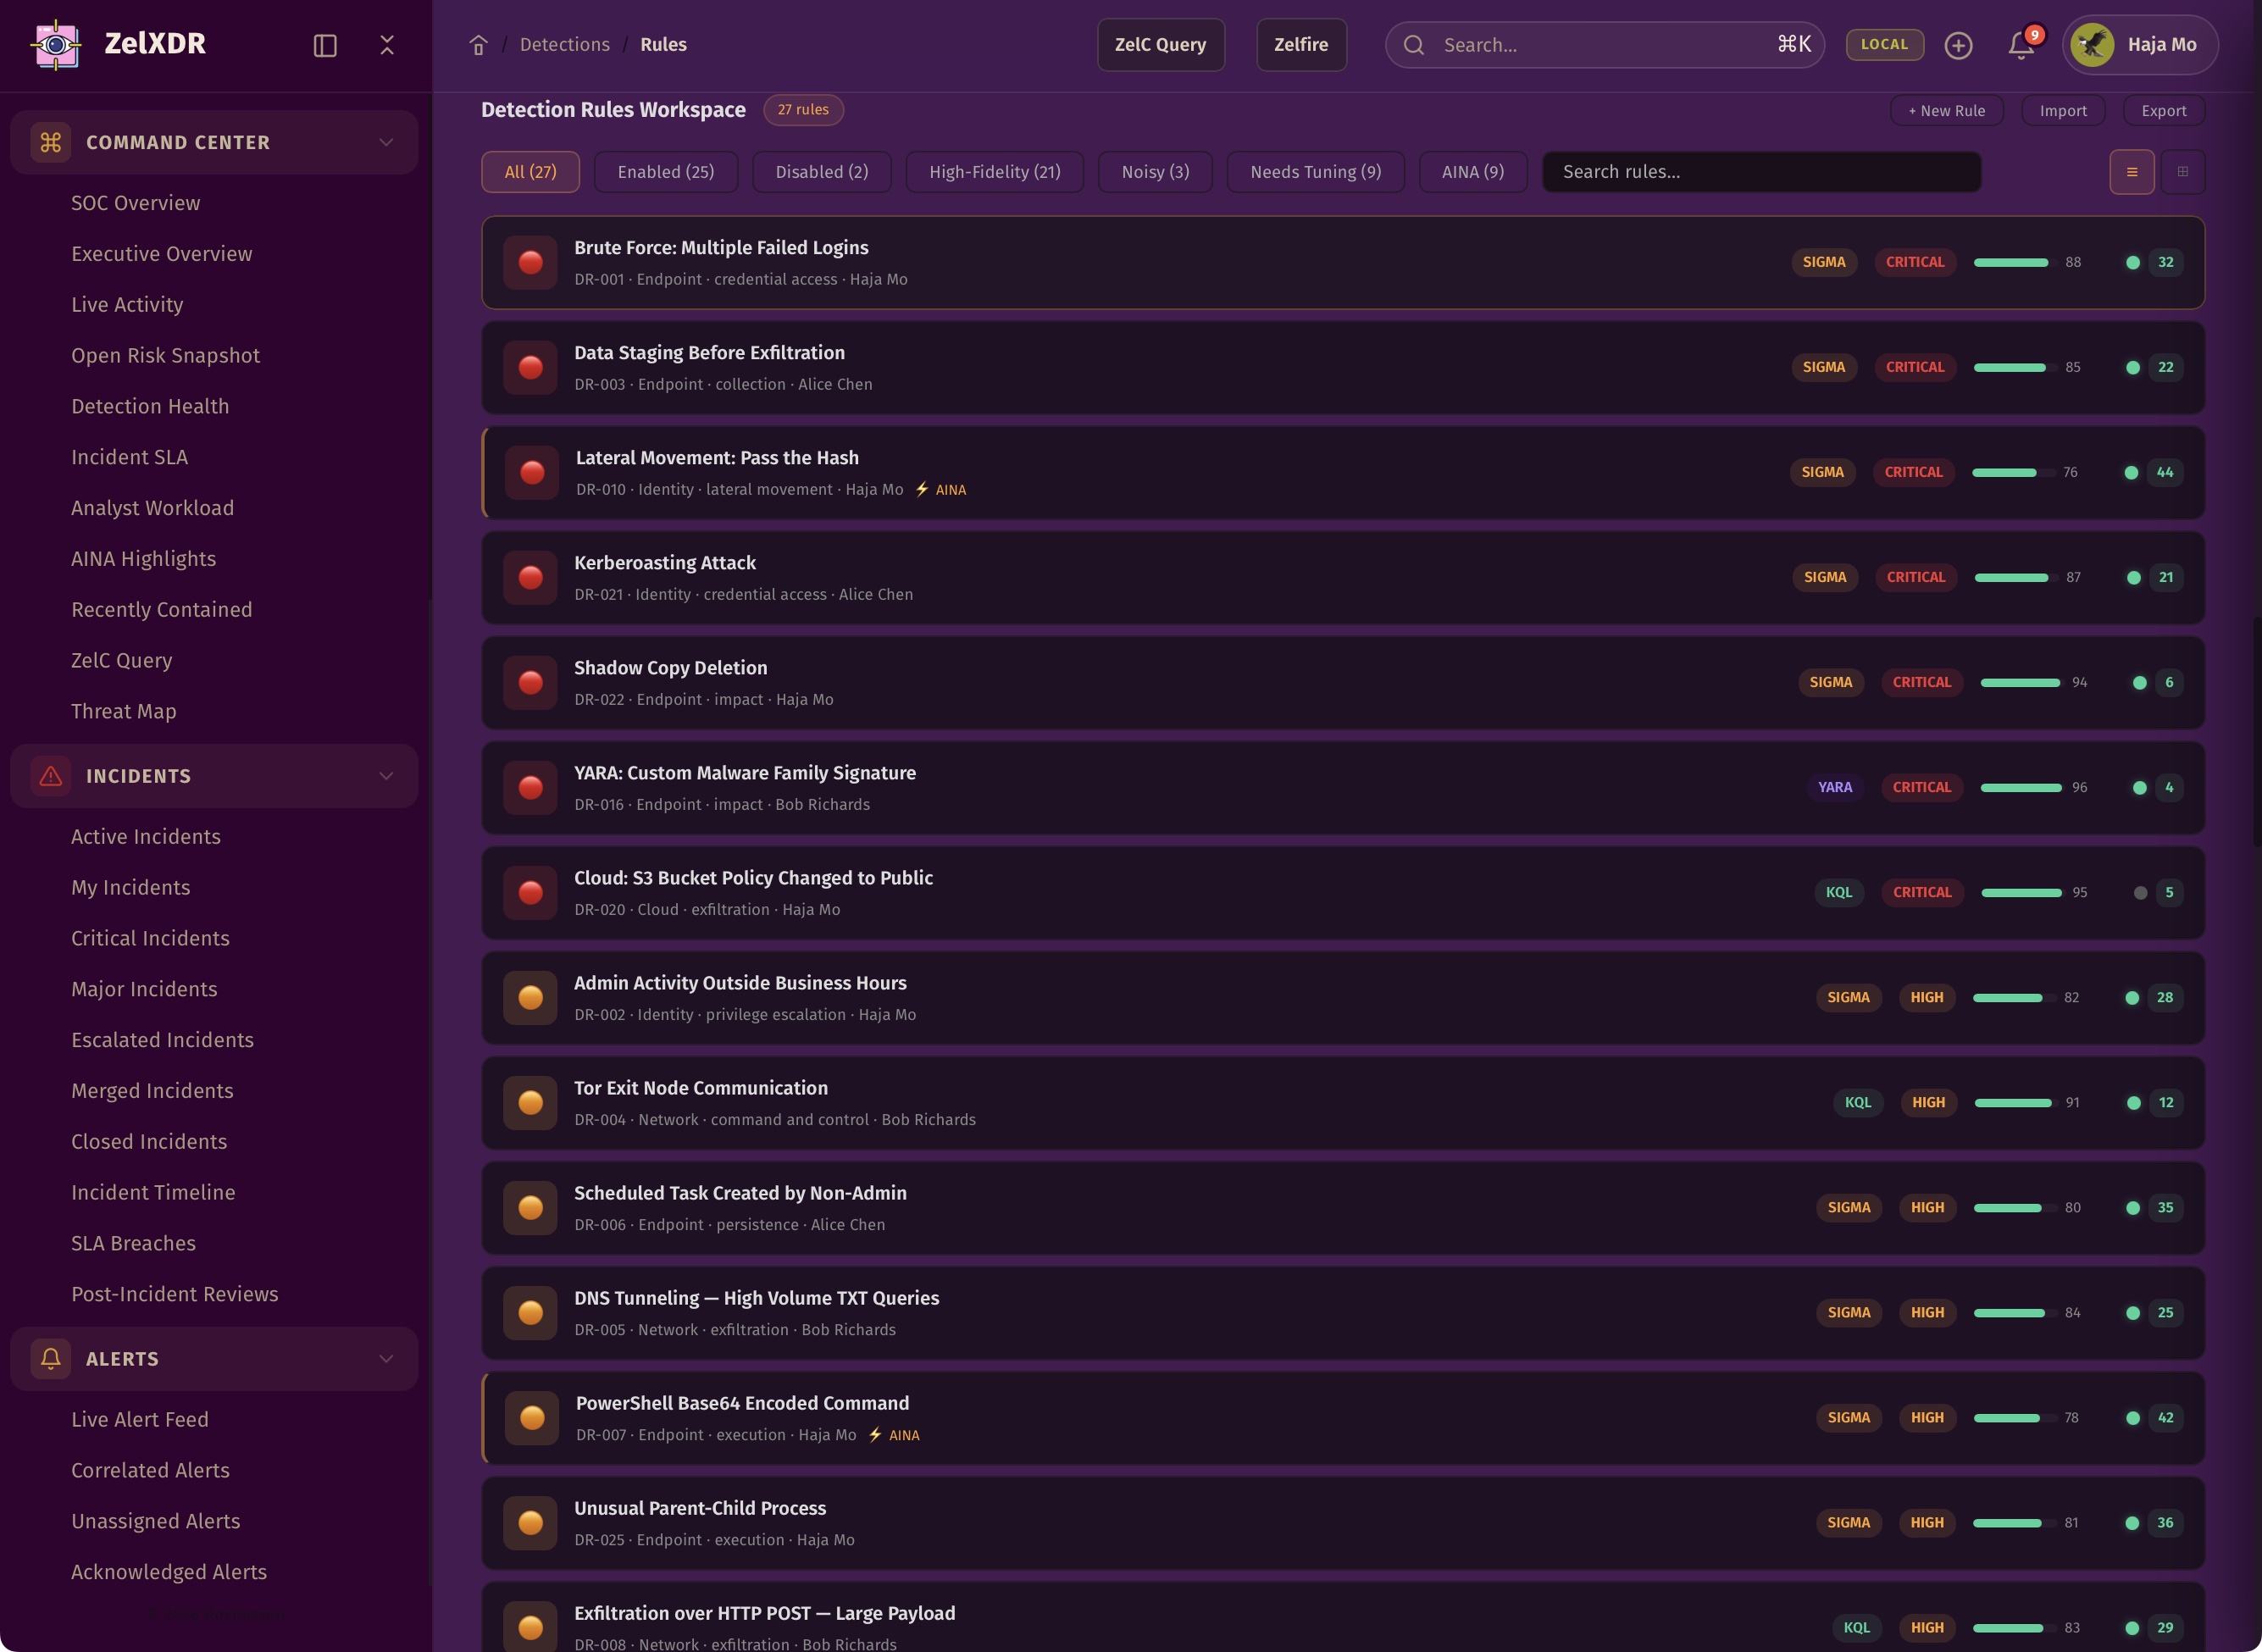
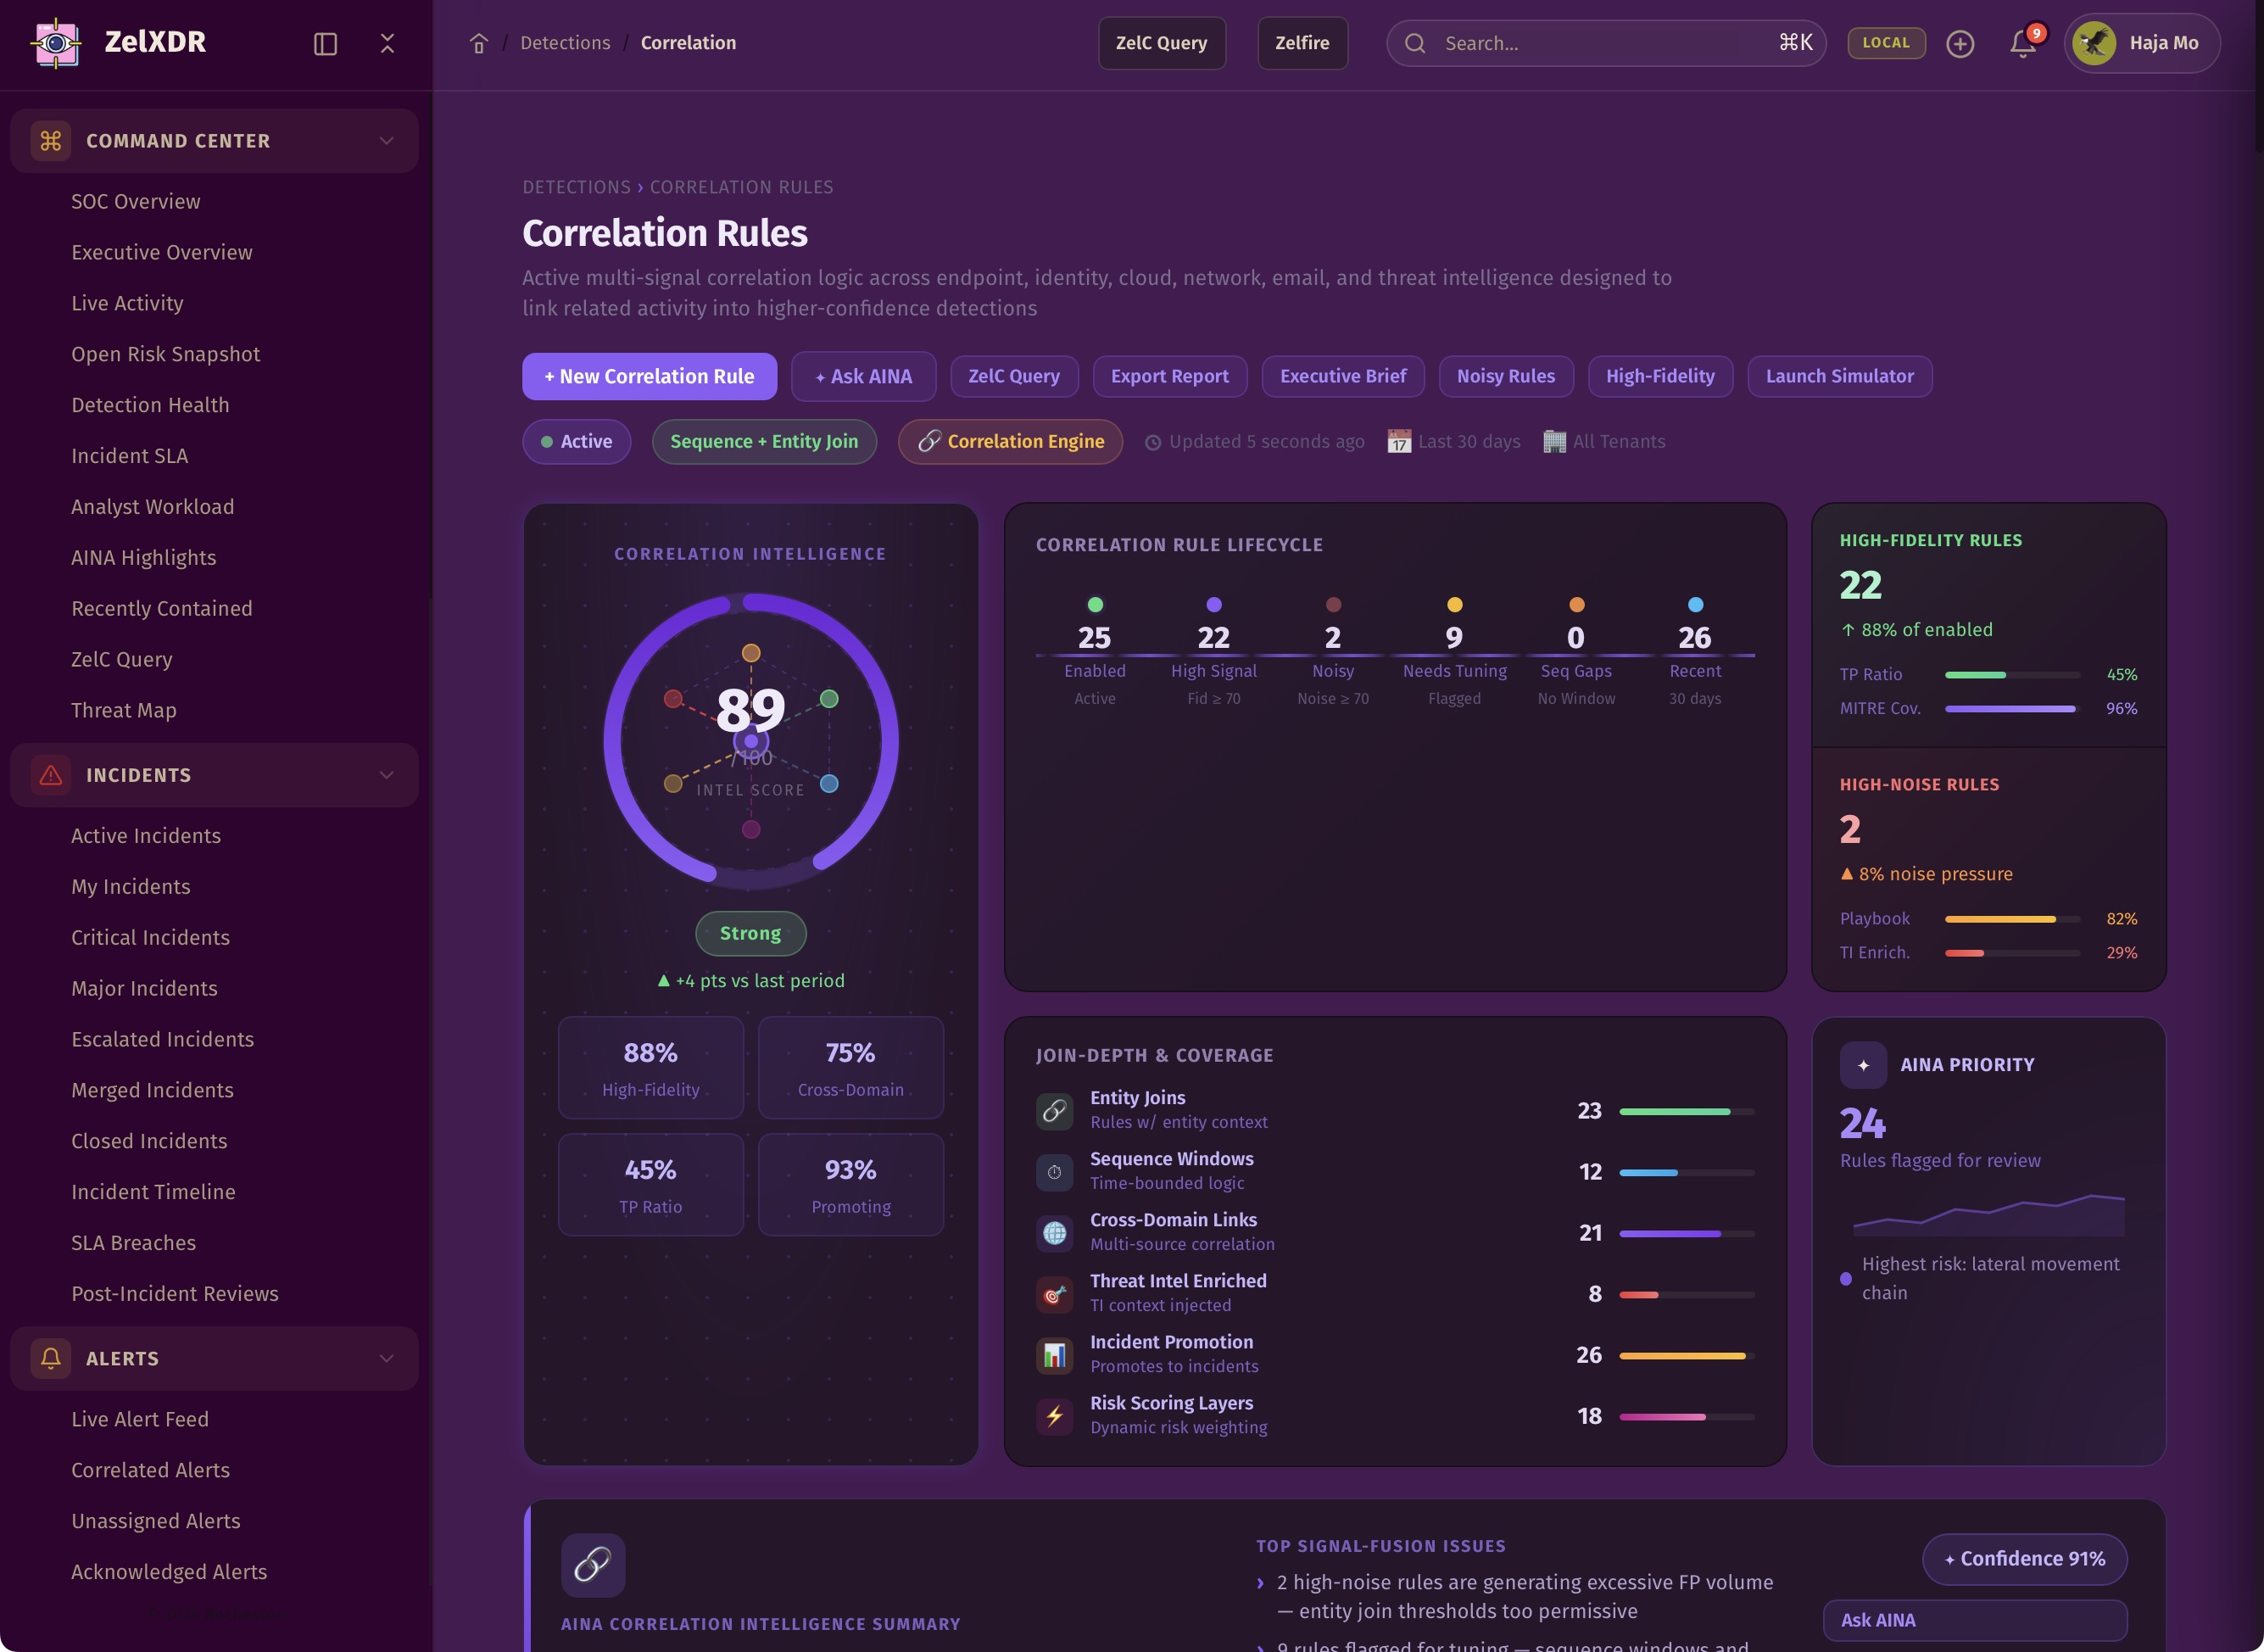
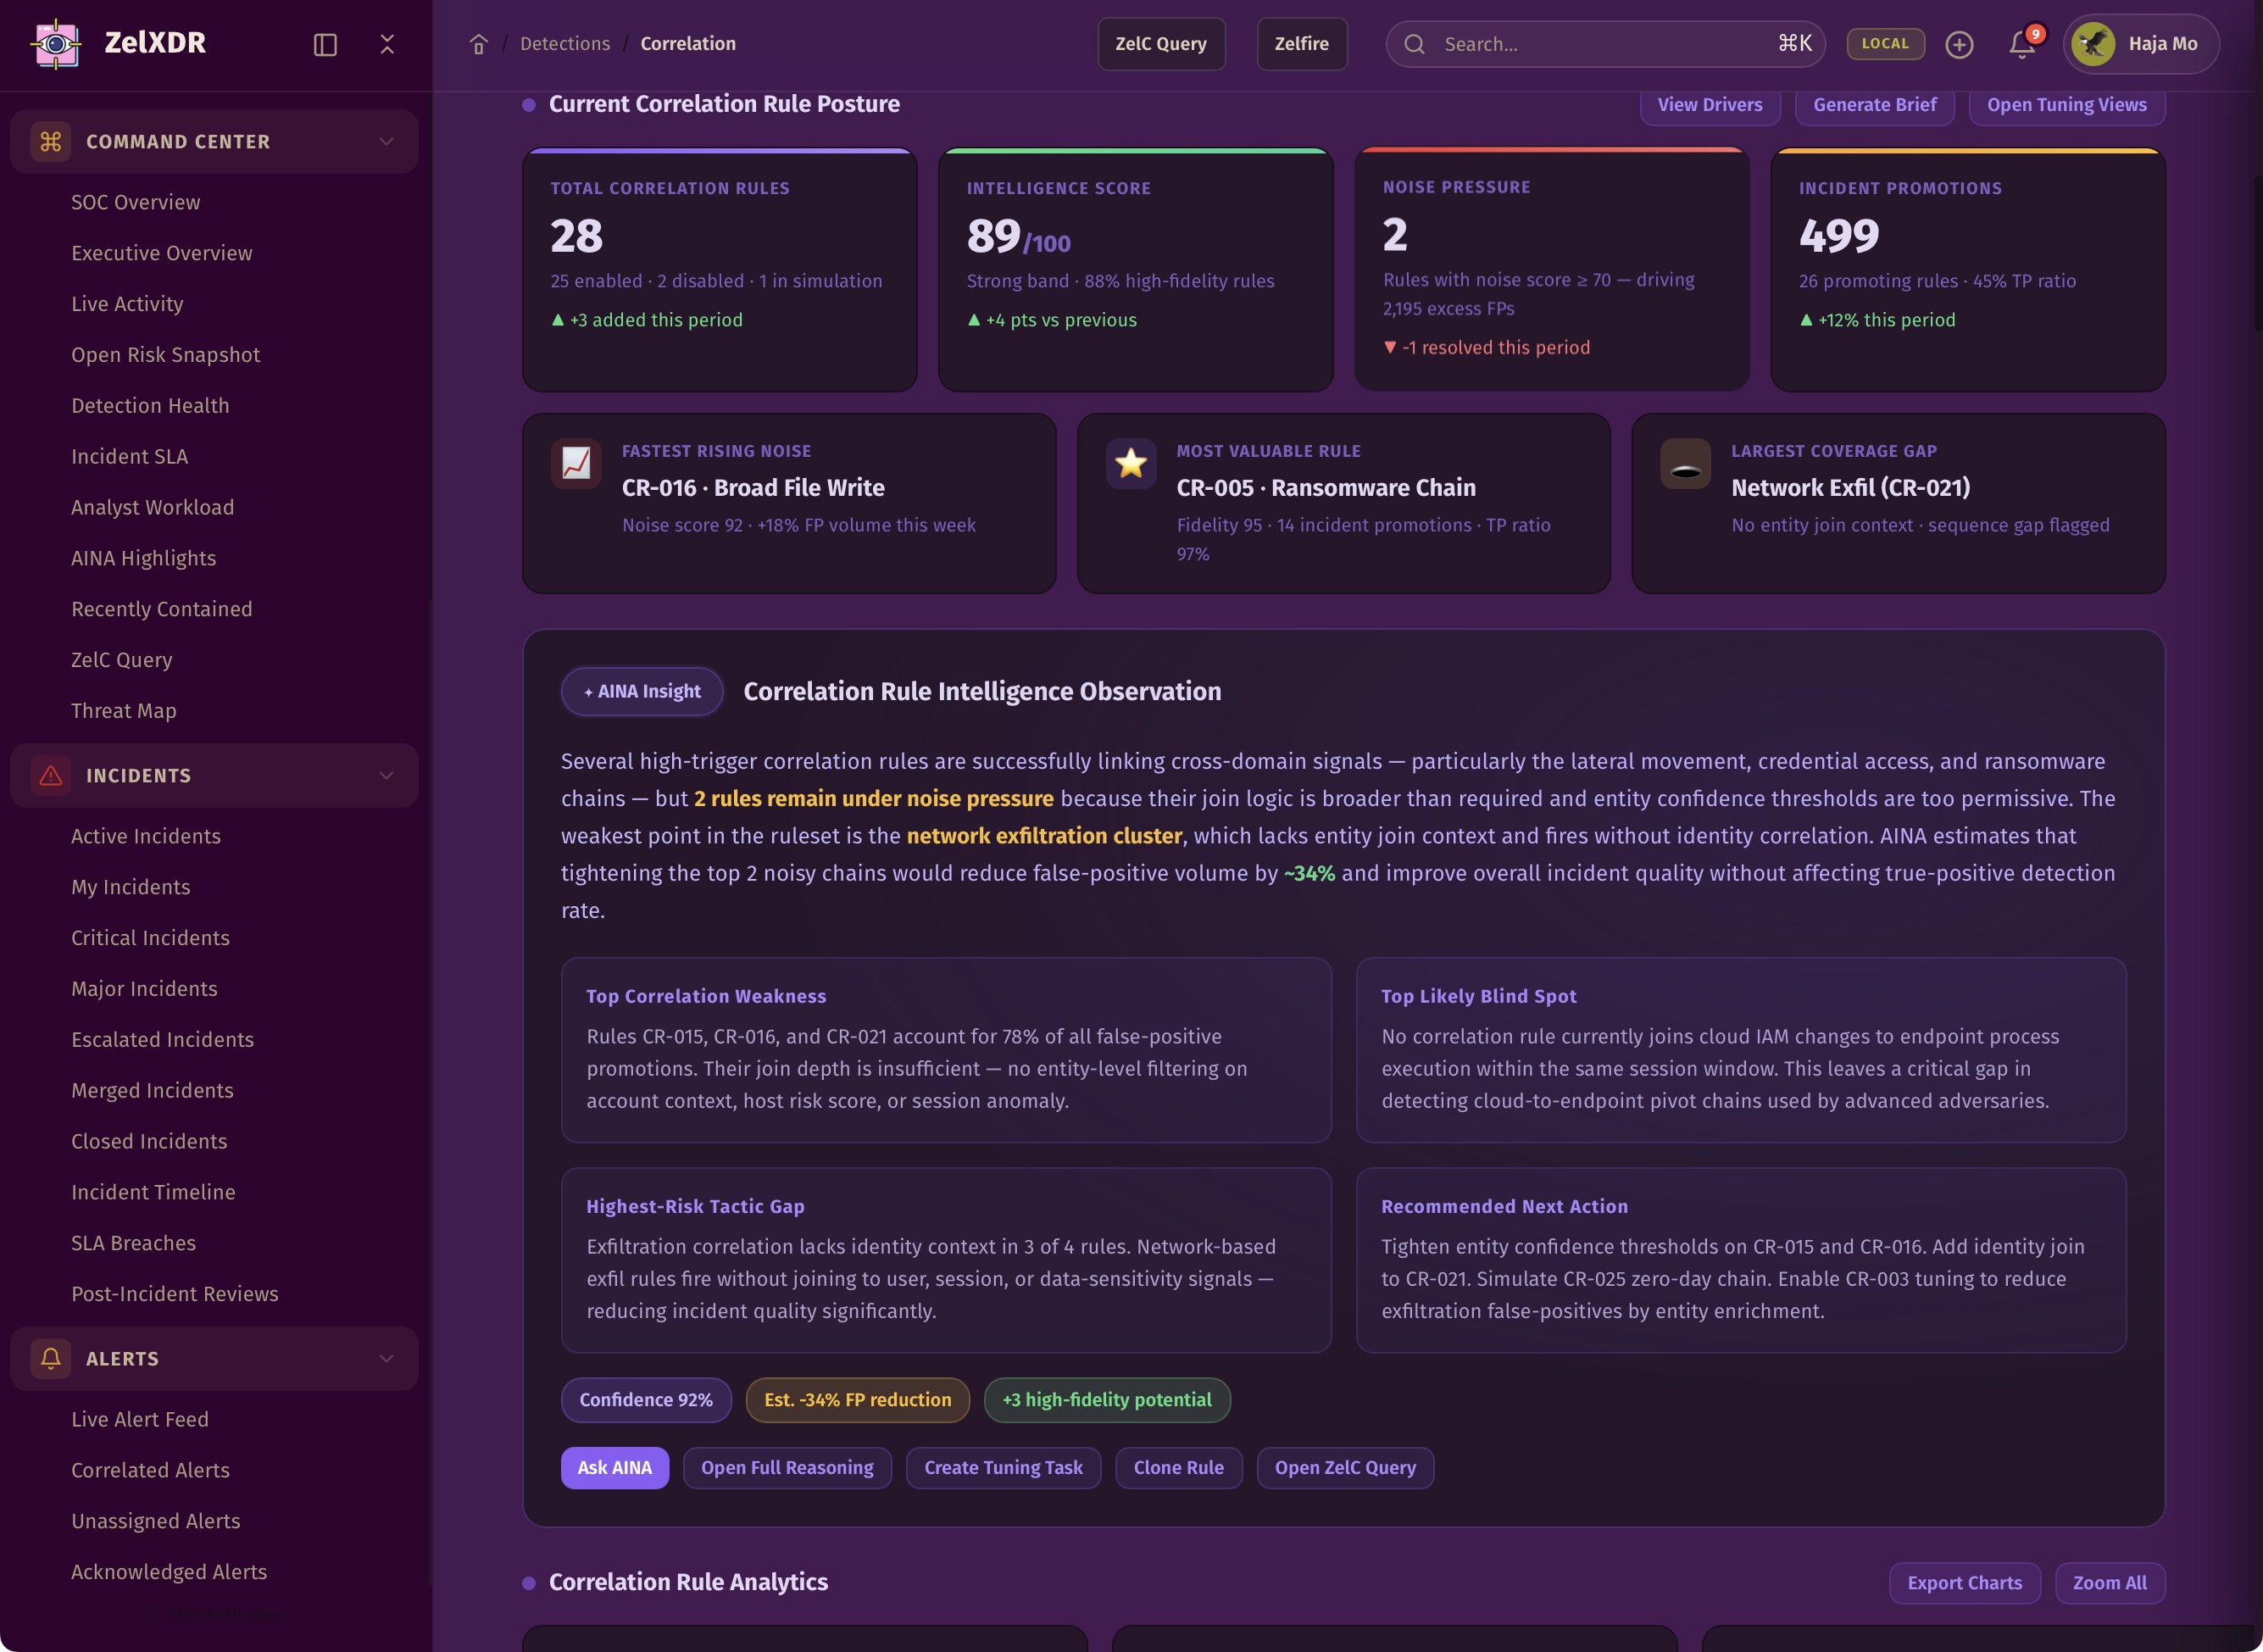
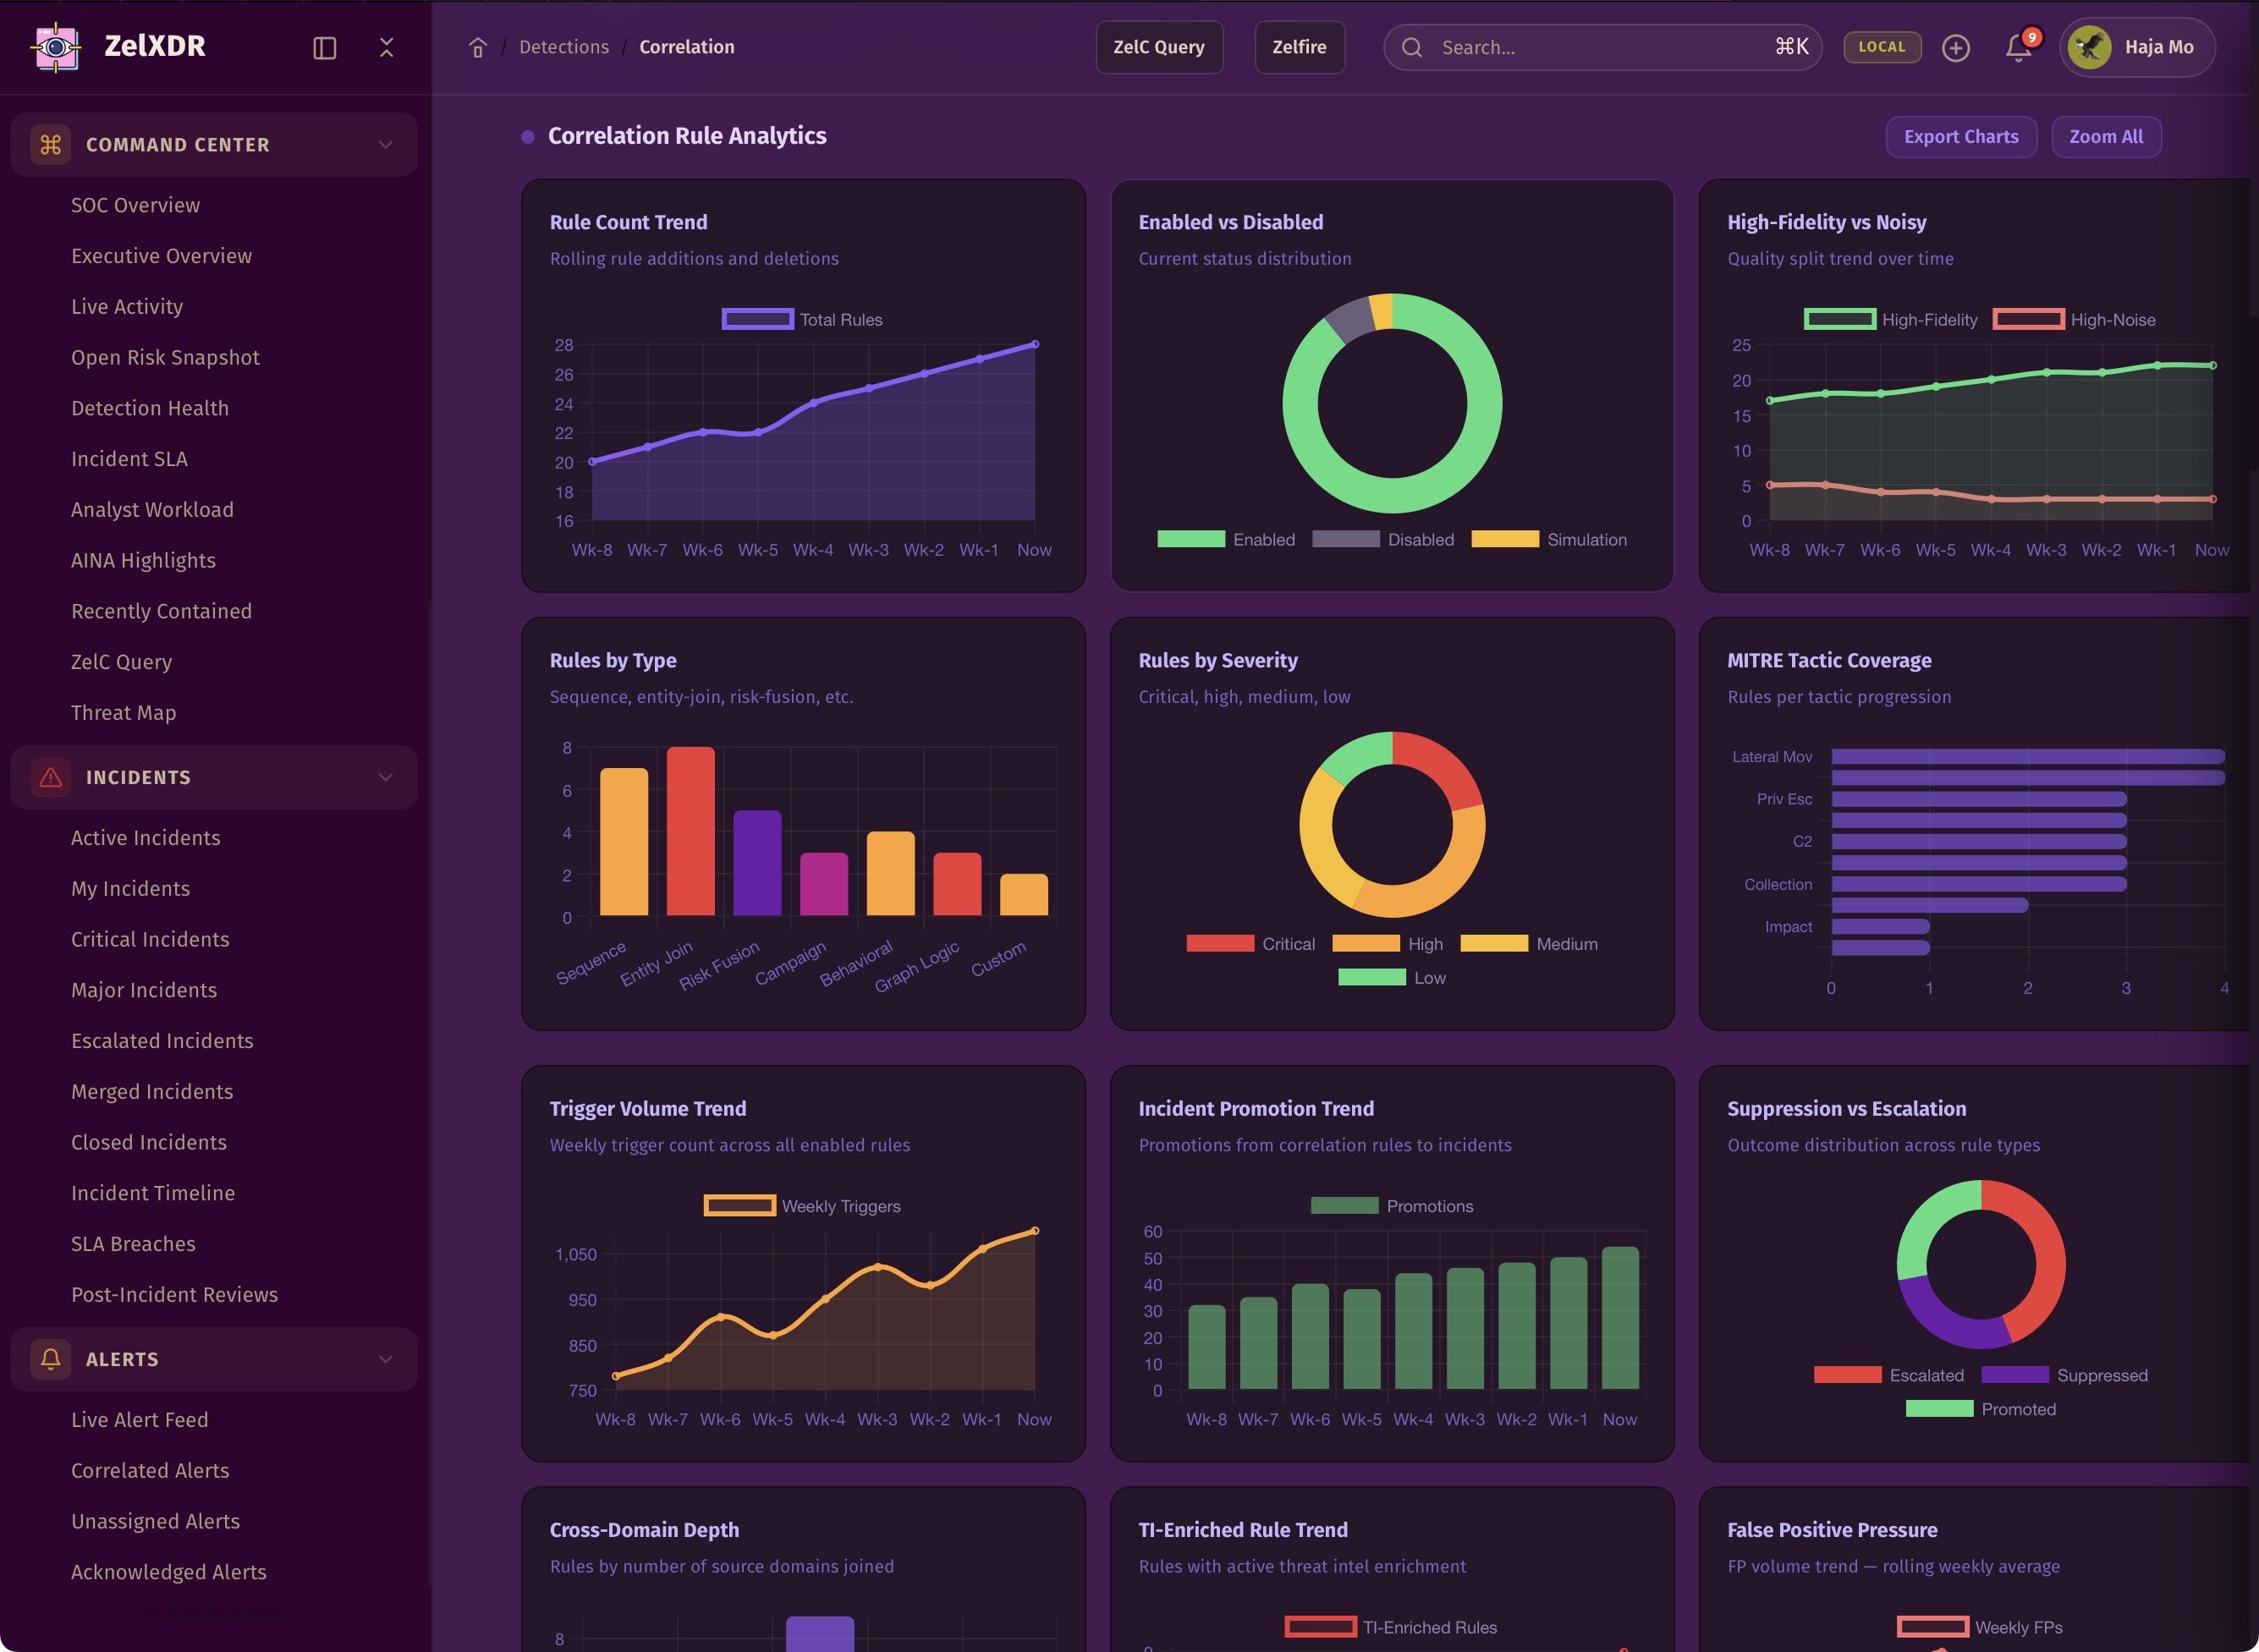
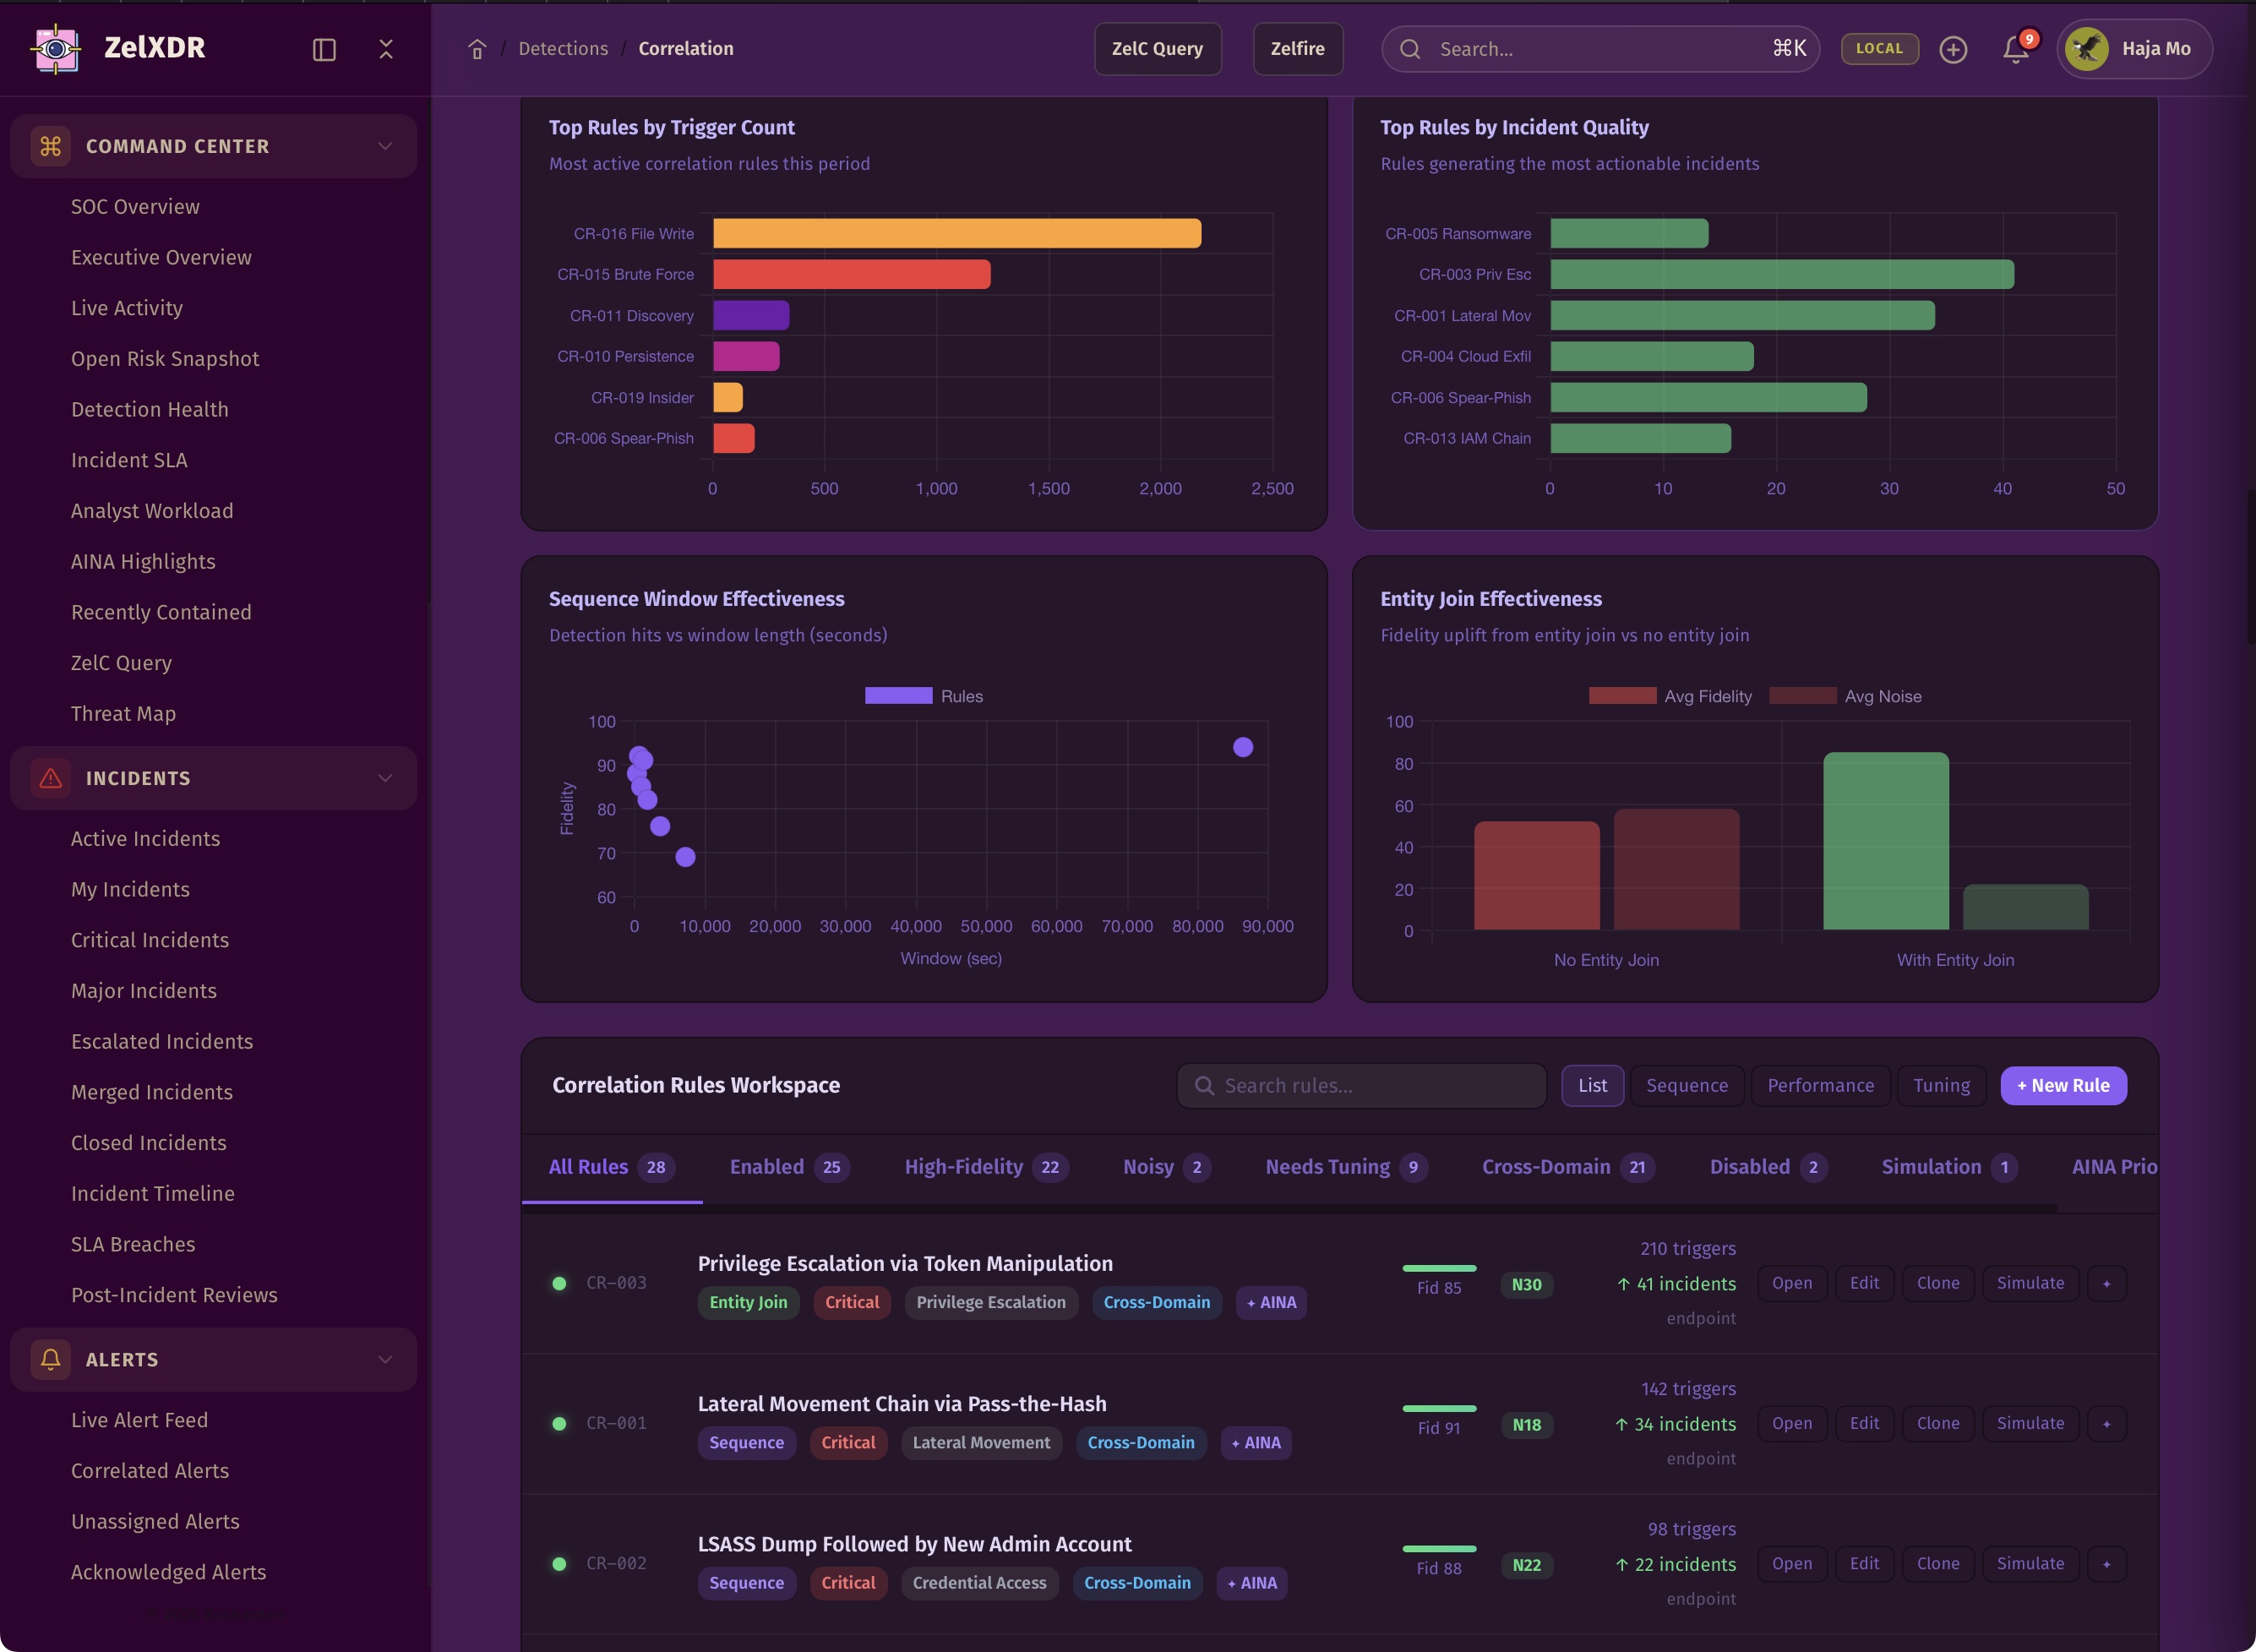
ZelXDR provides a home for detection logic that is measurable, reviewable, and continuously improved. Teams can build coverage while tracking noise, quality, and operational value.
Great detections are refined, not guessed.
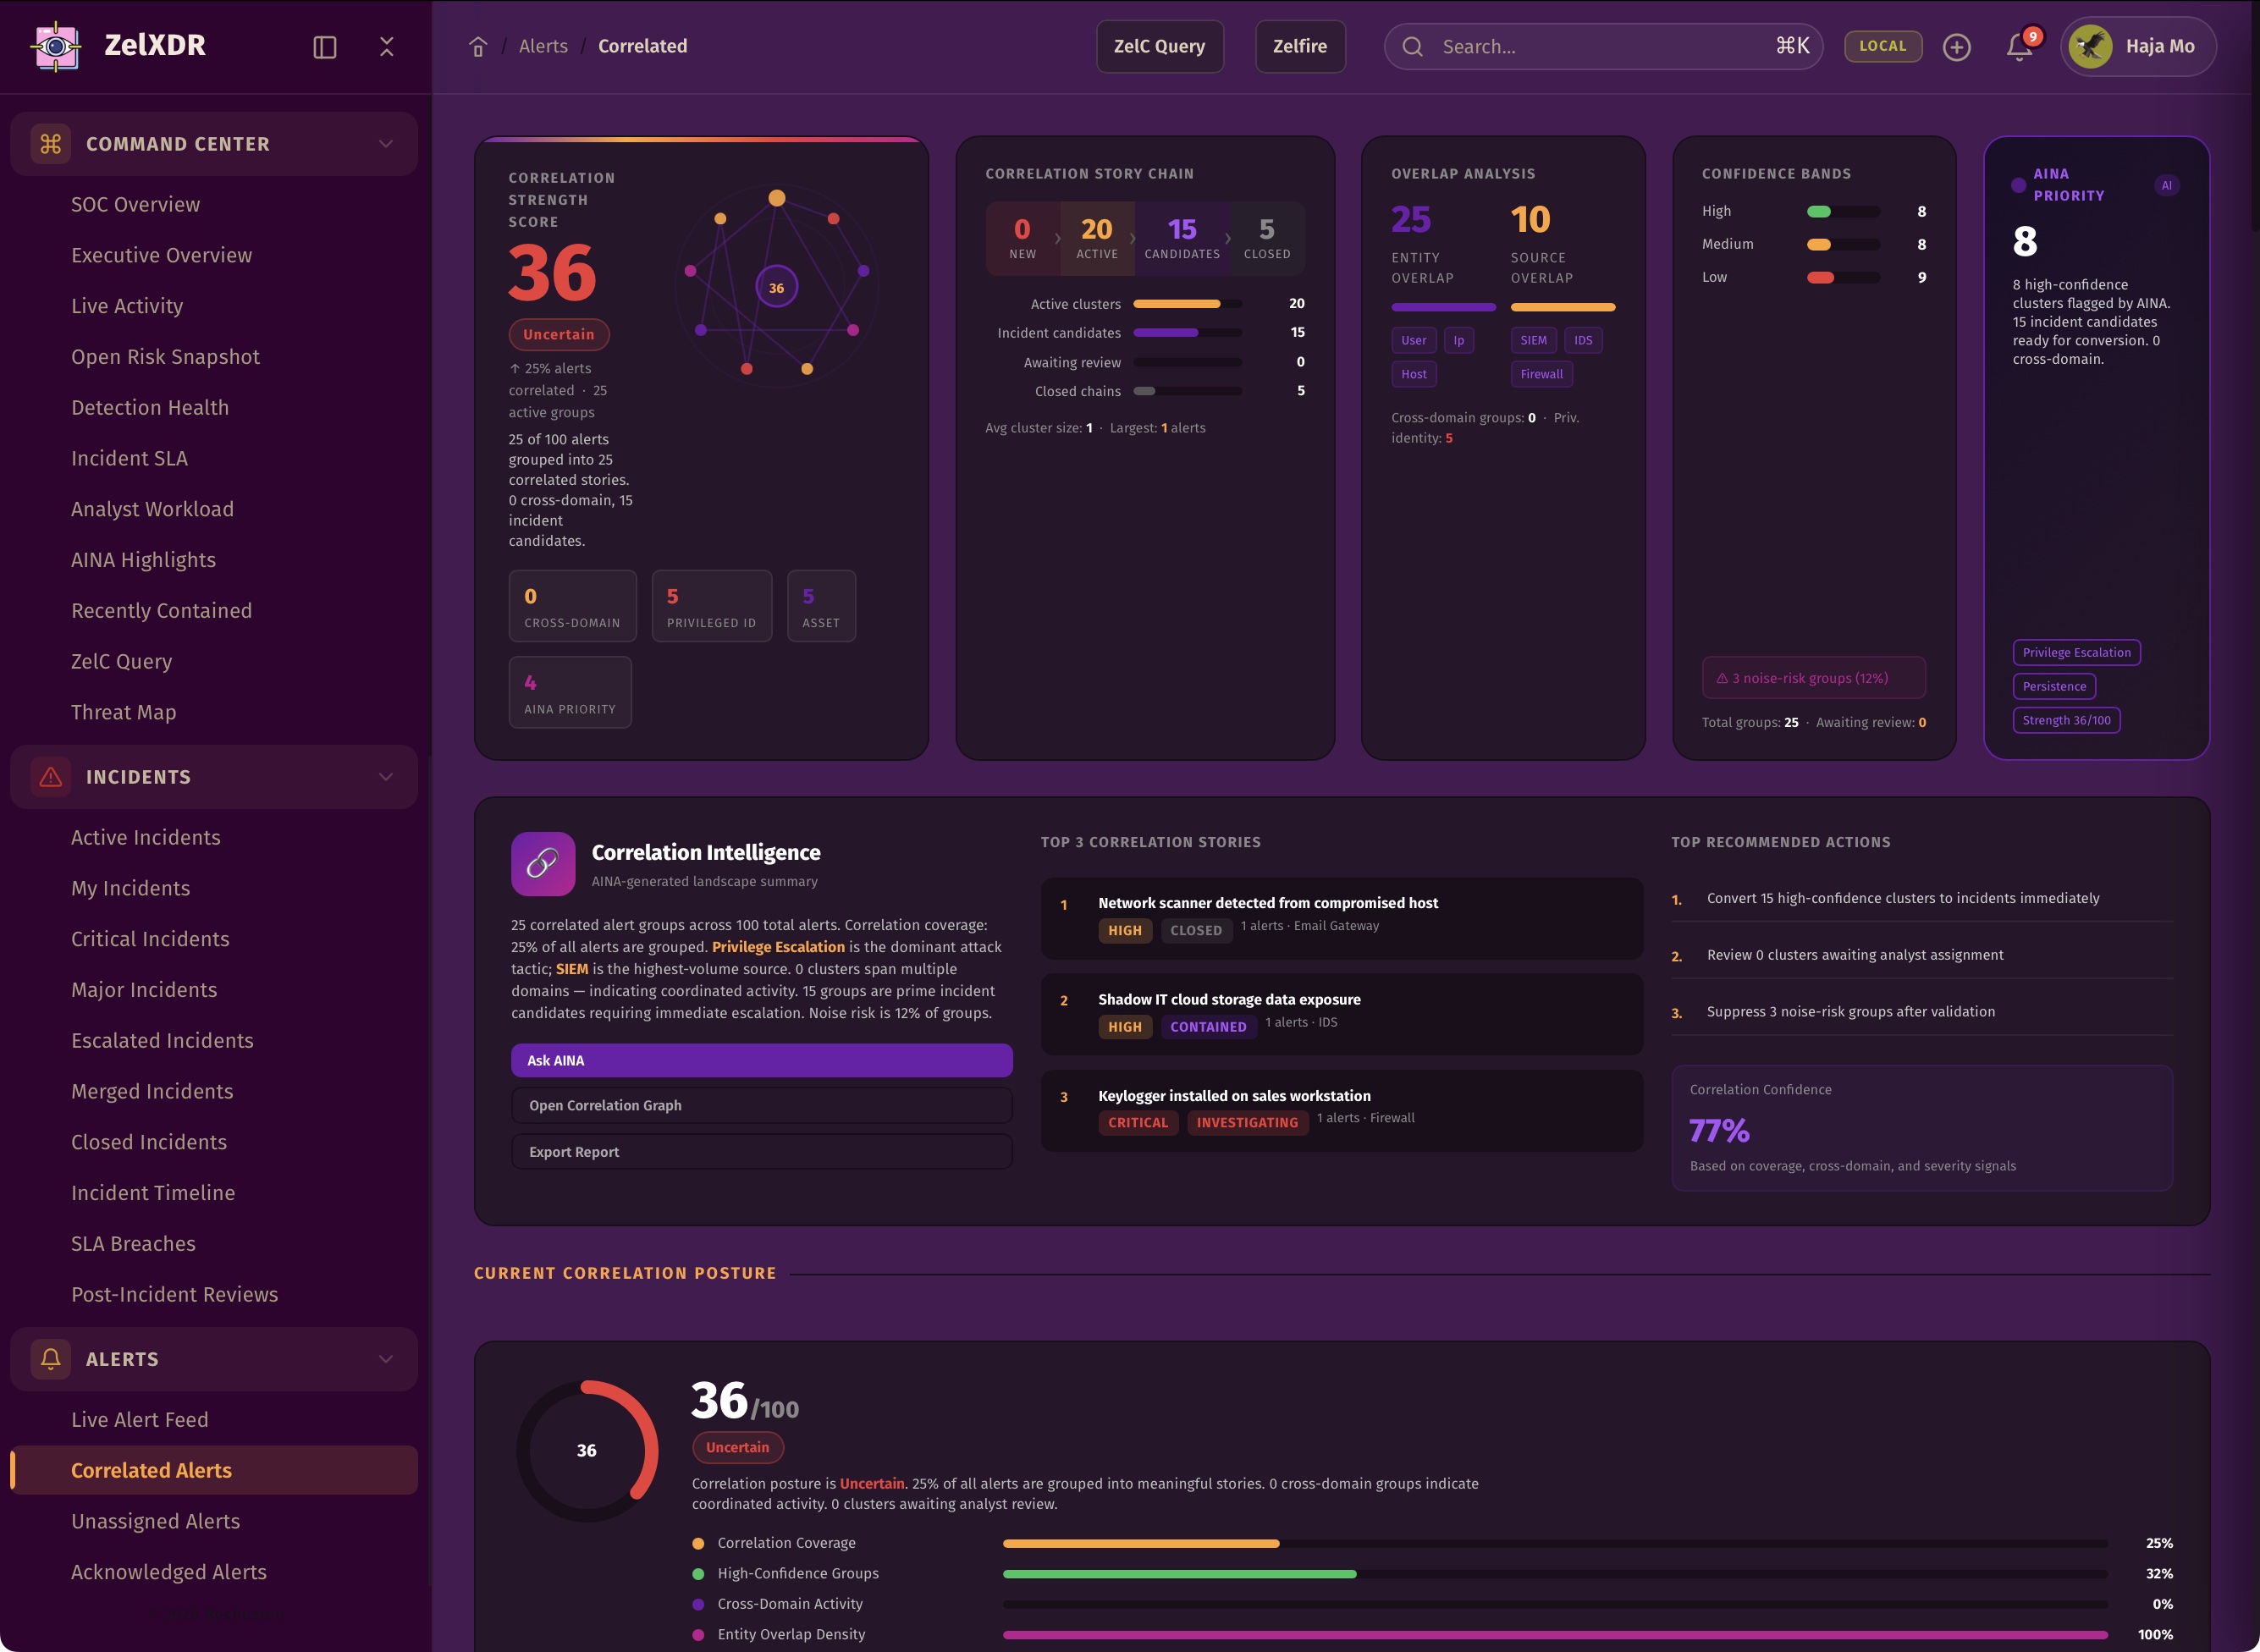
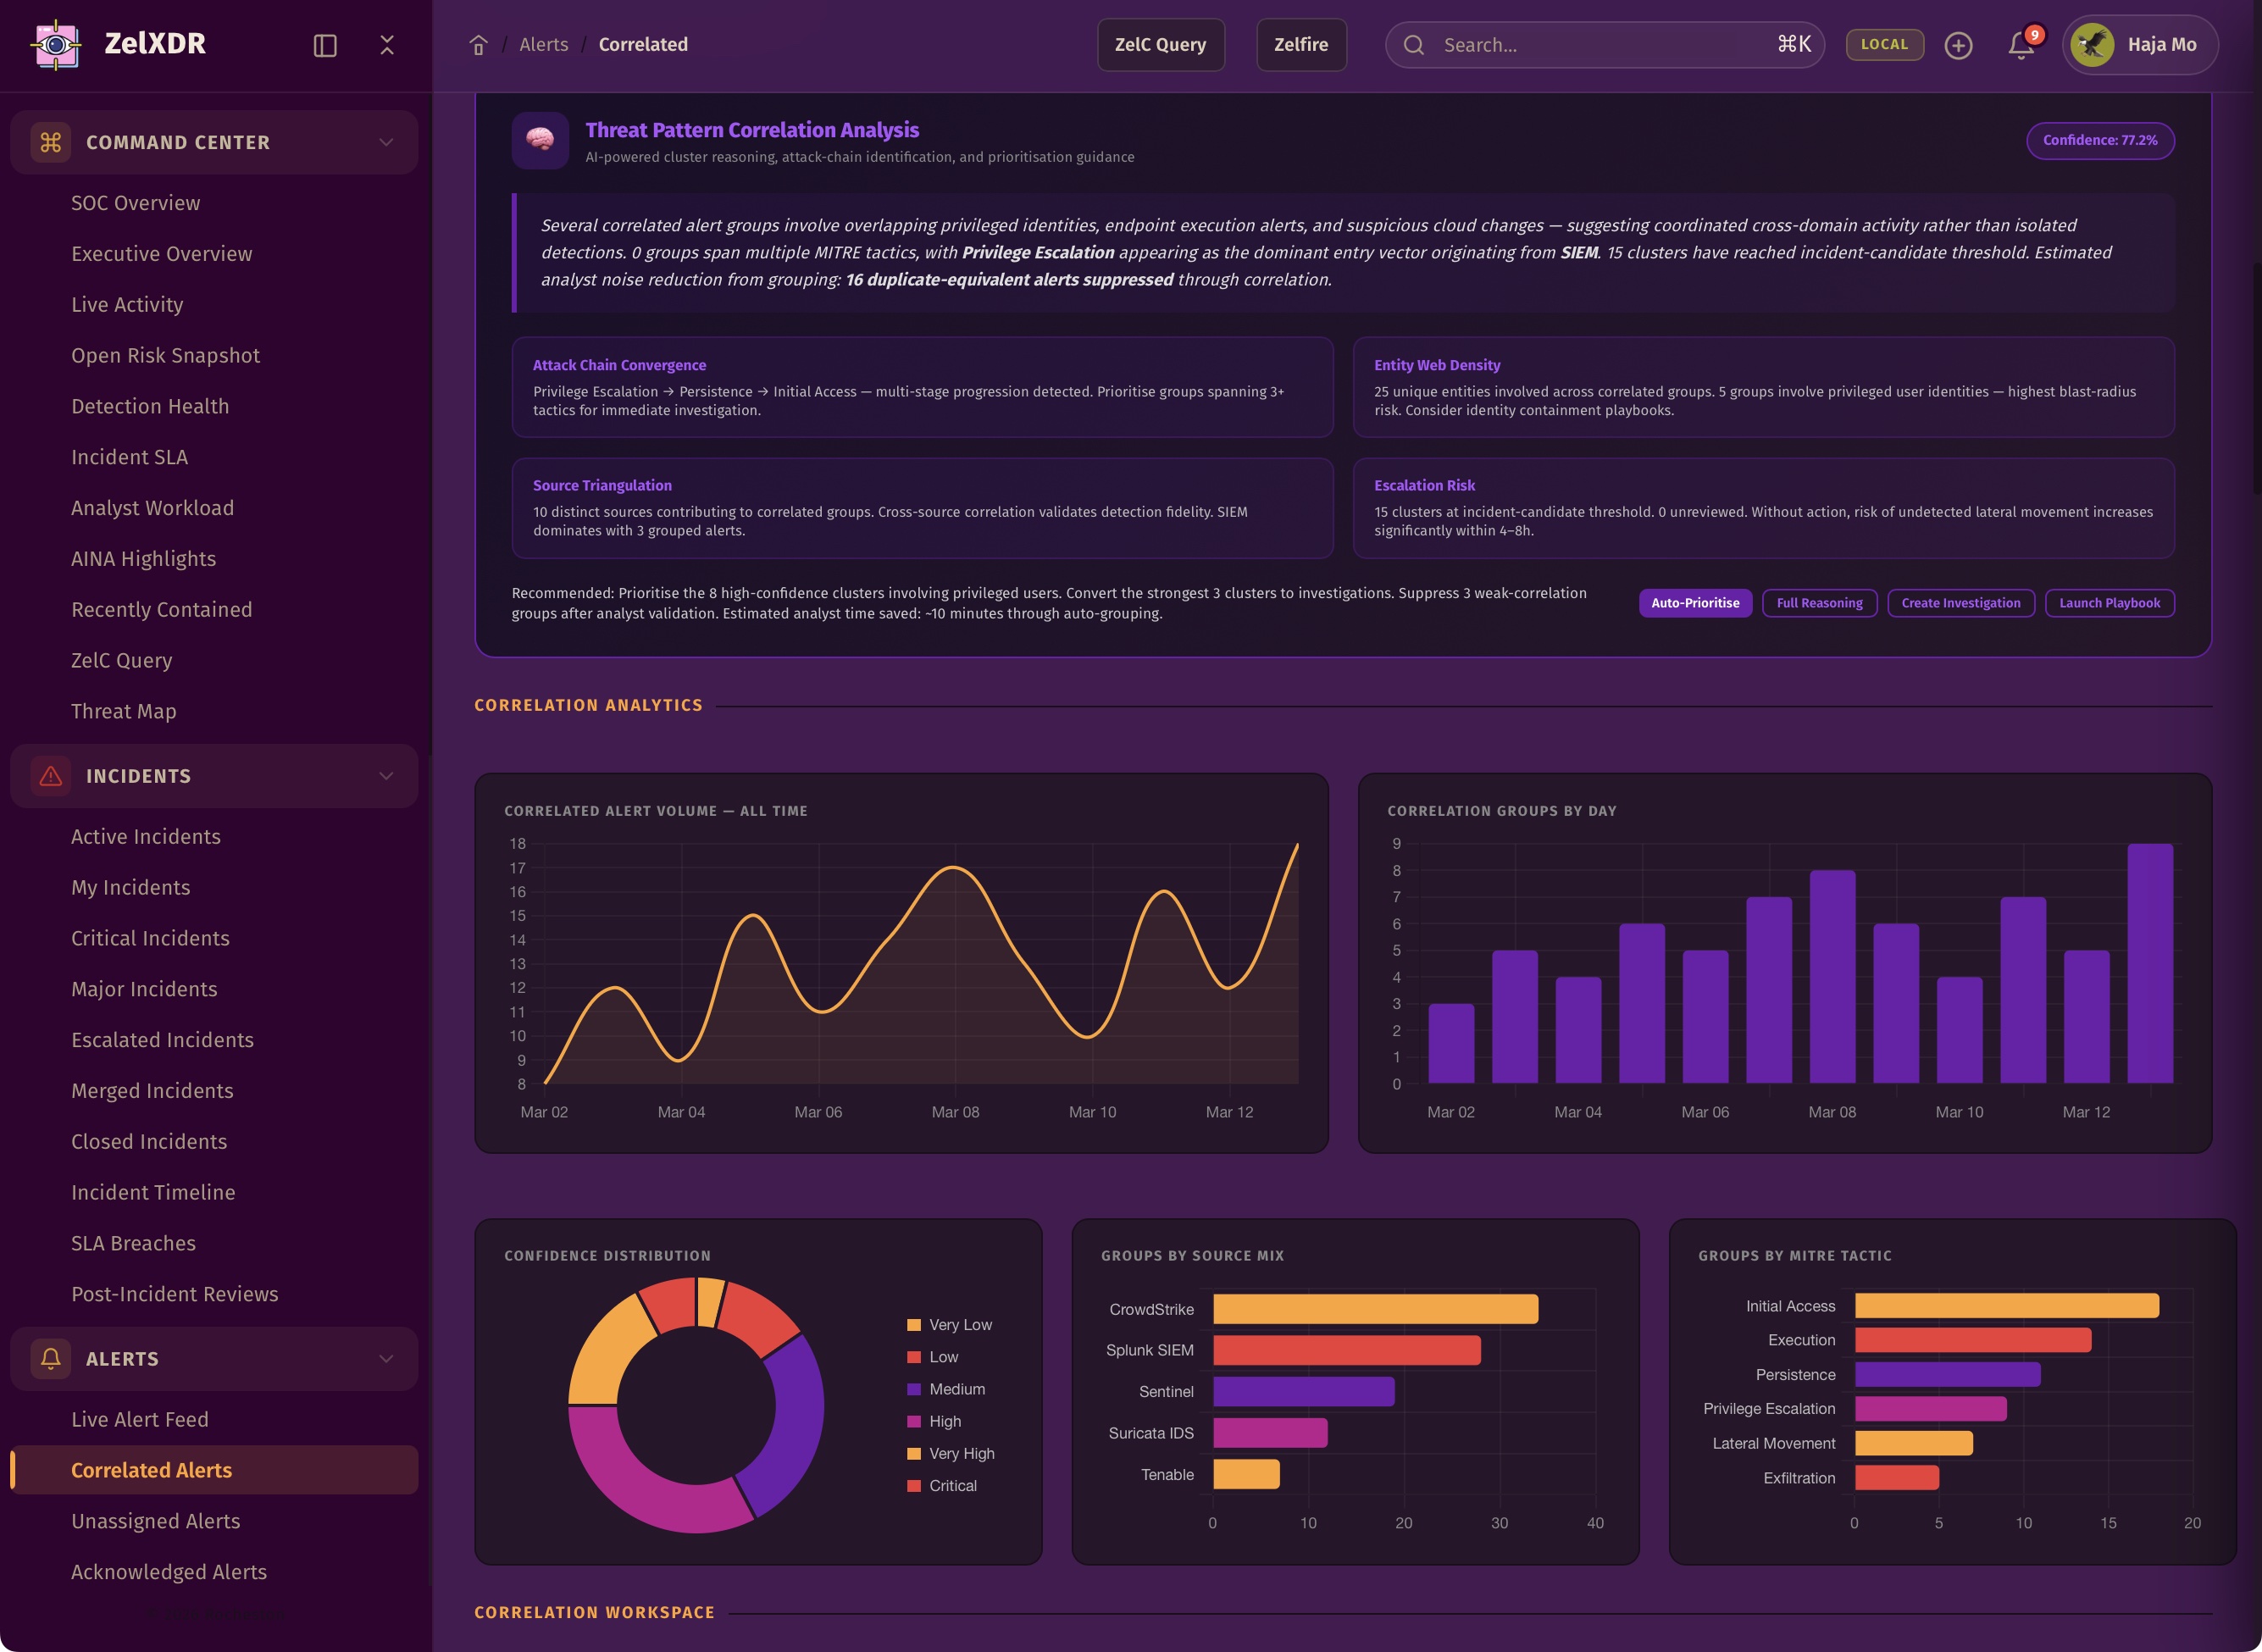
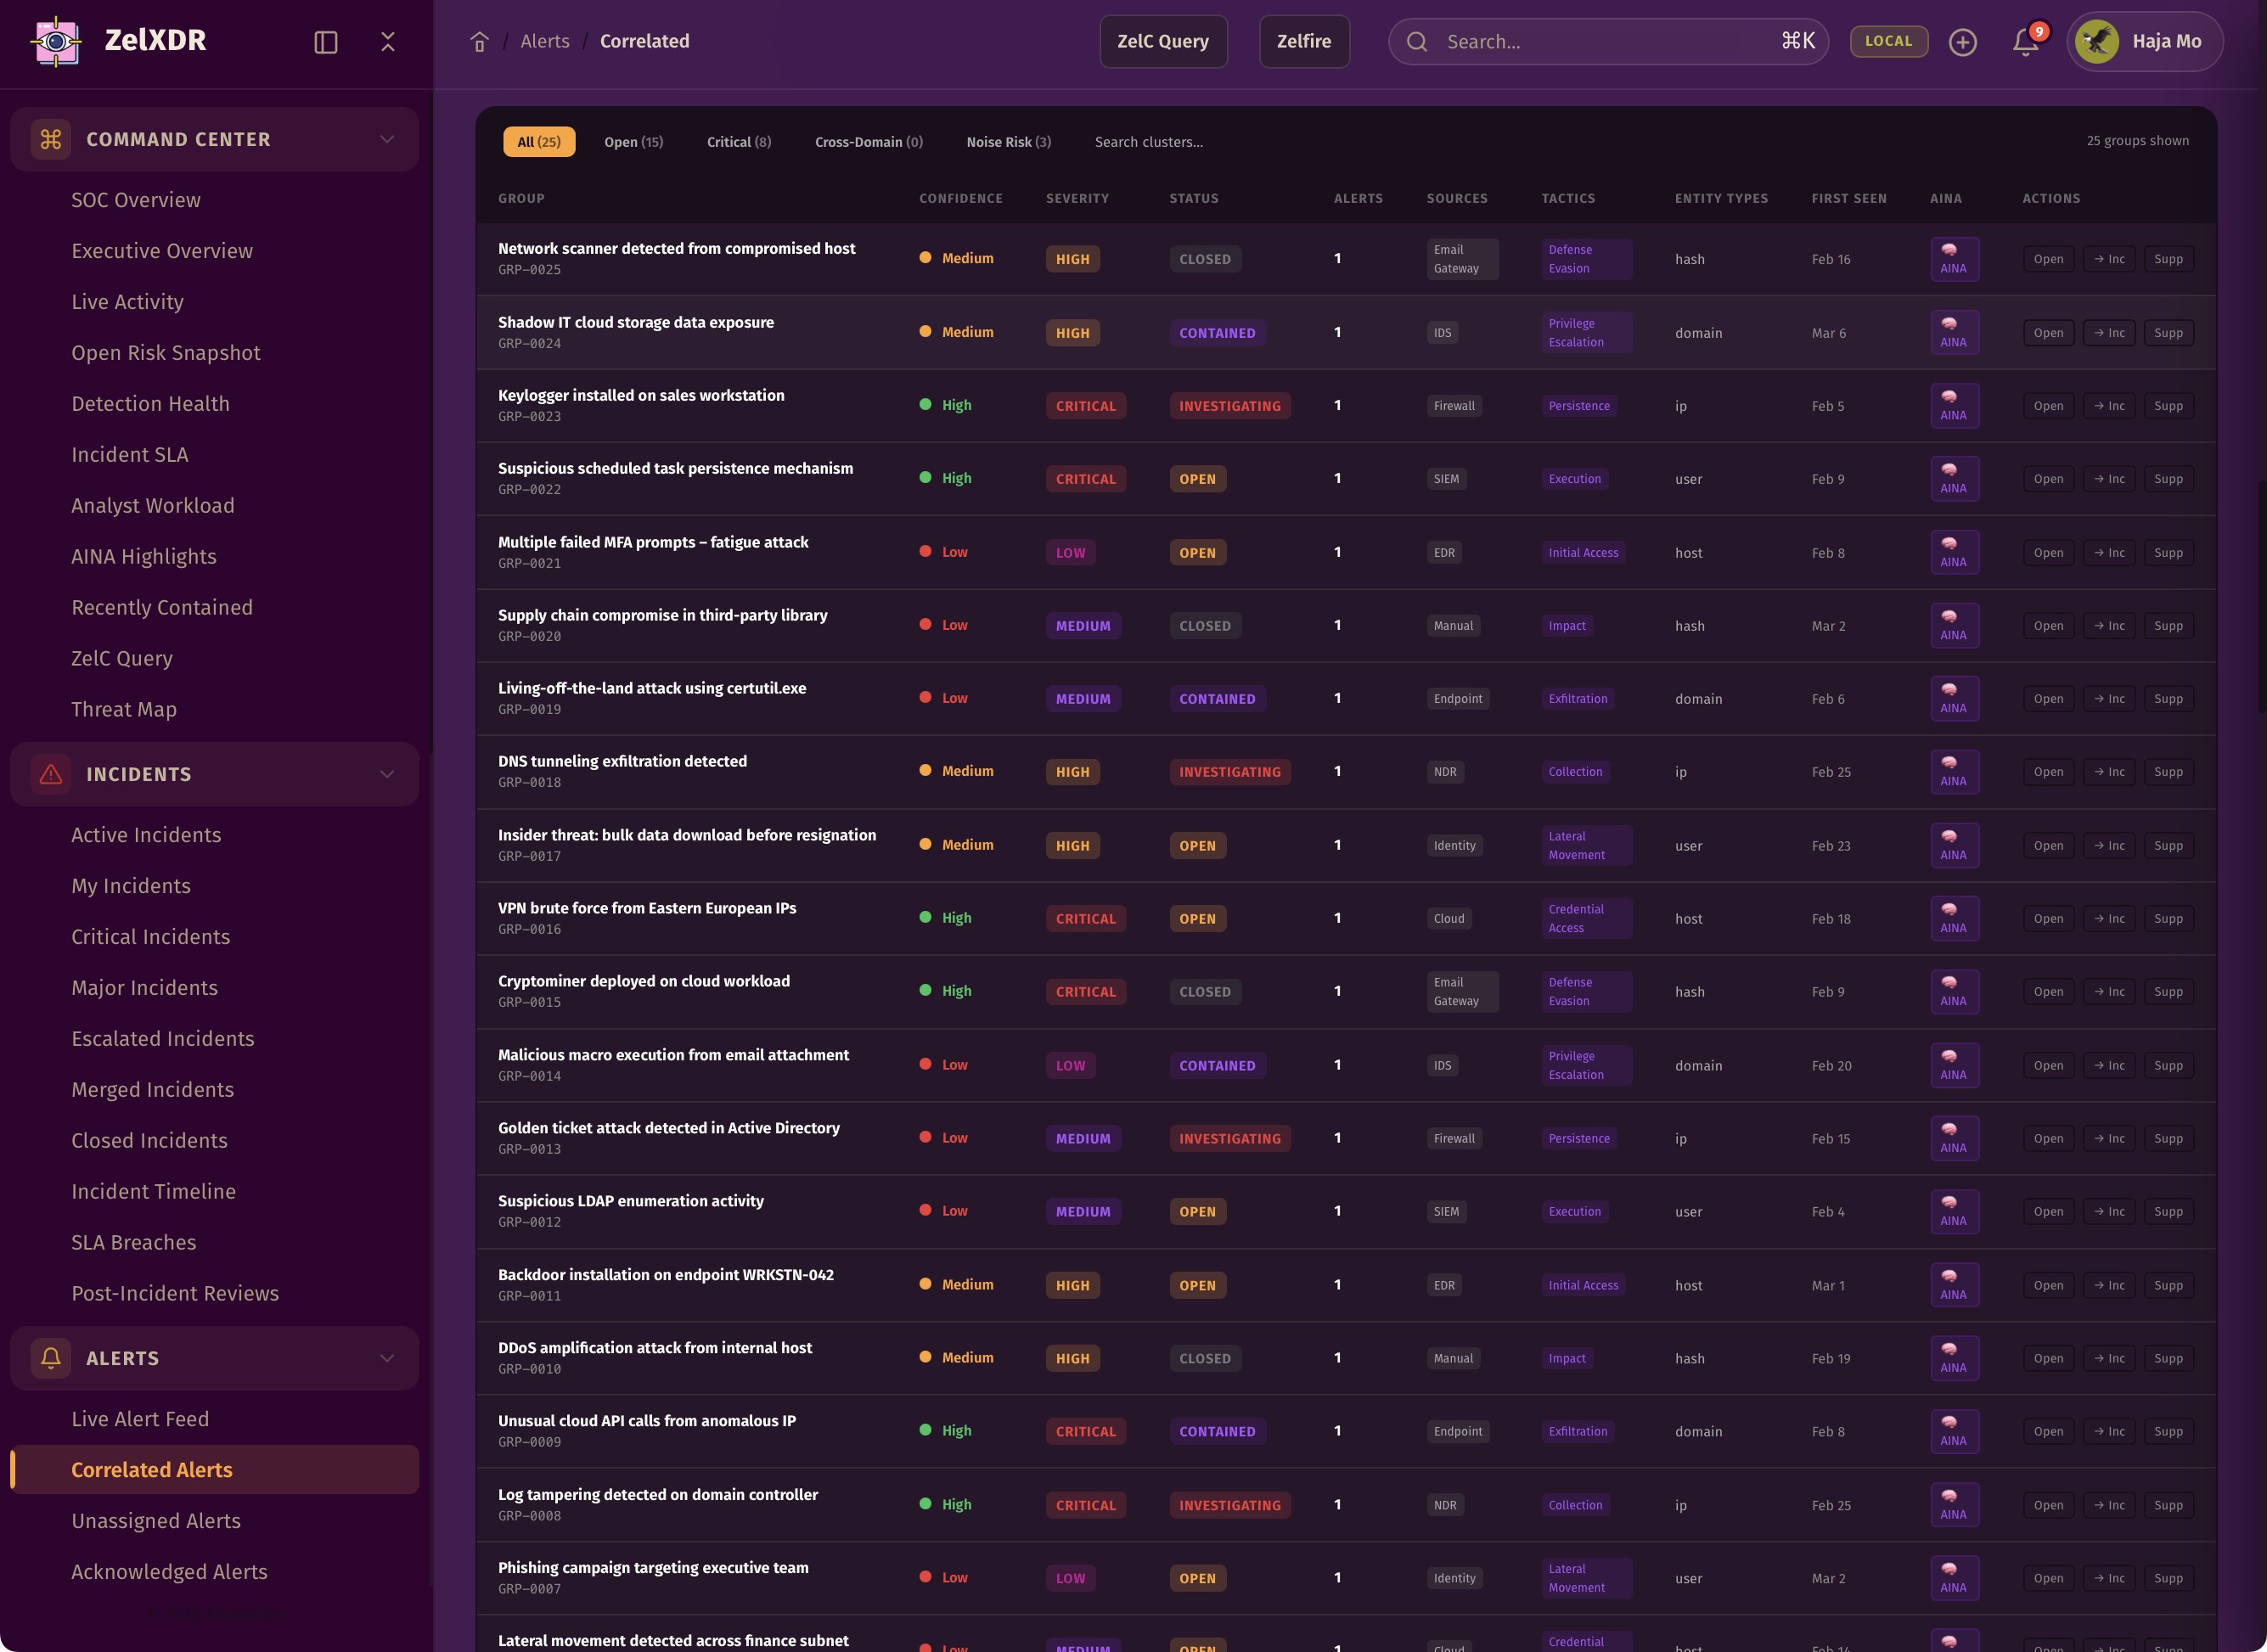
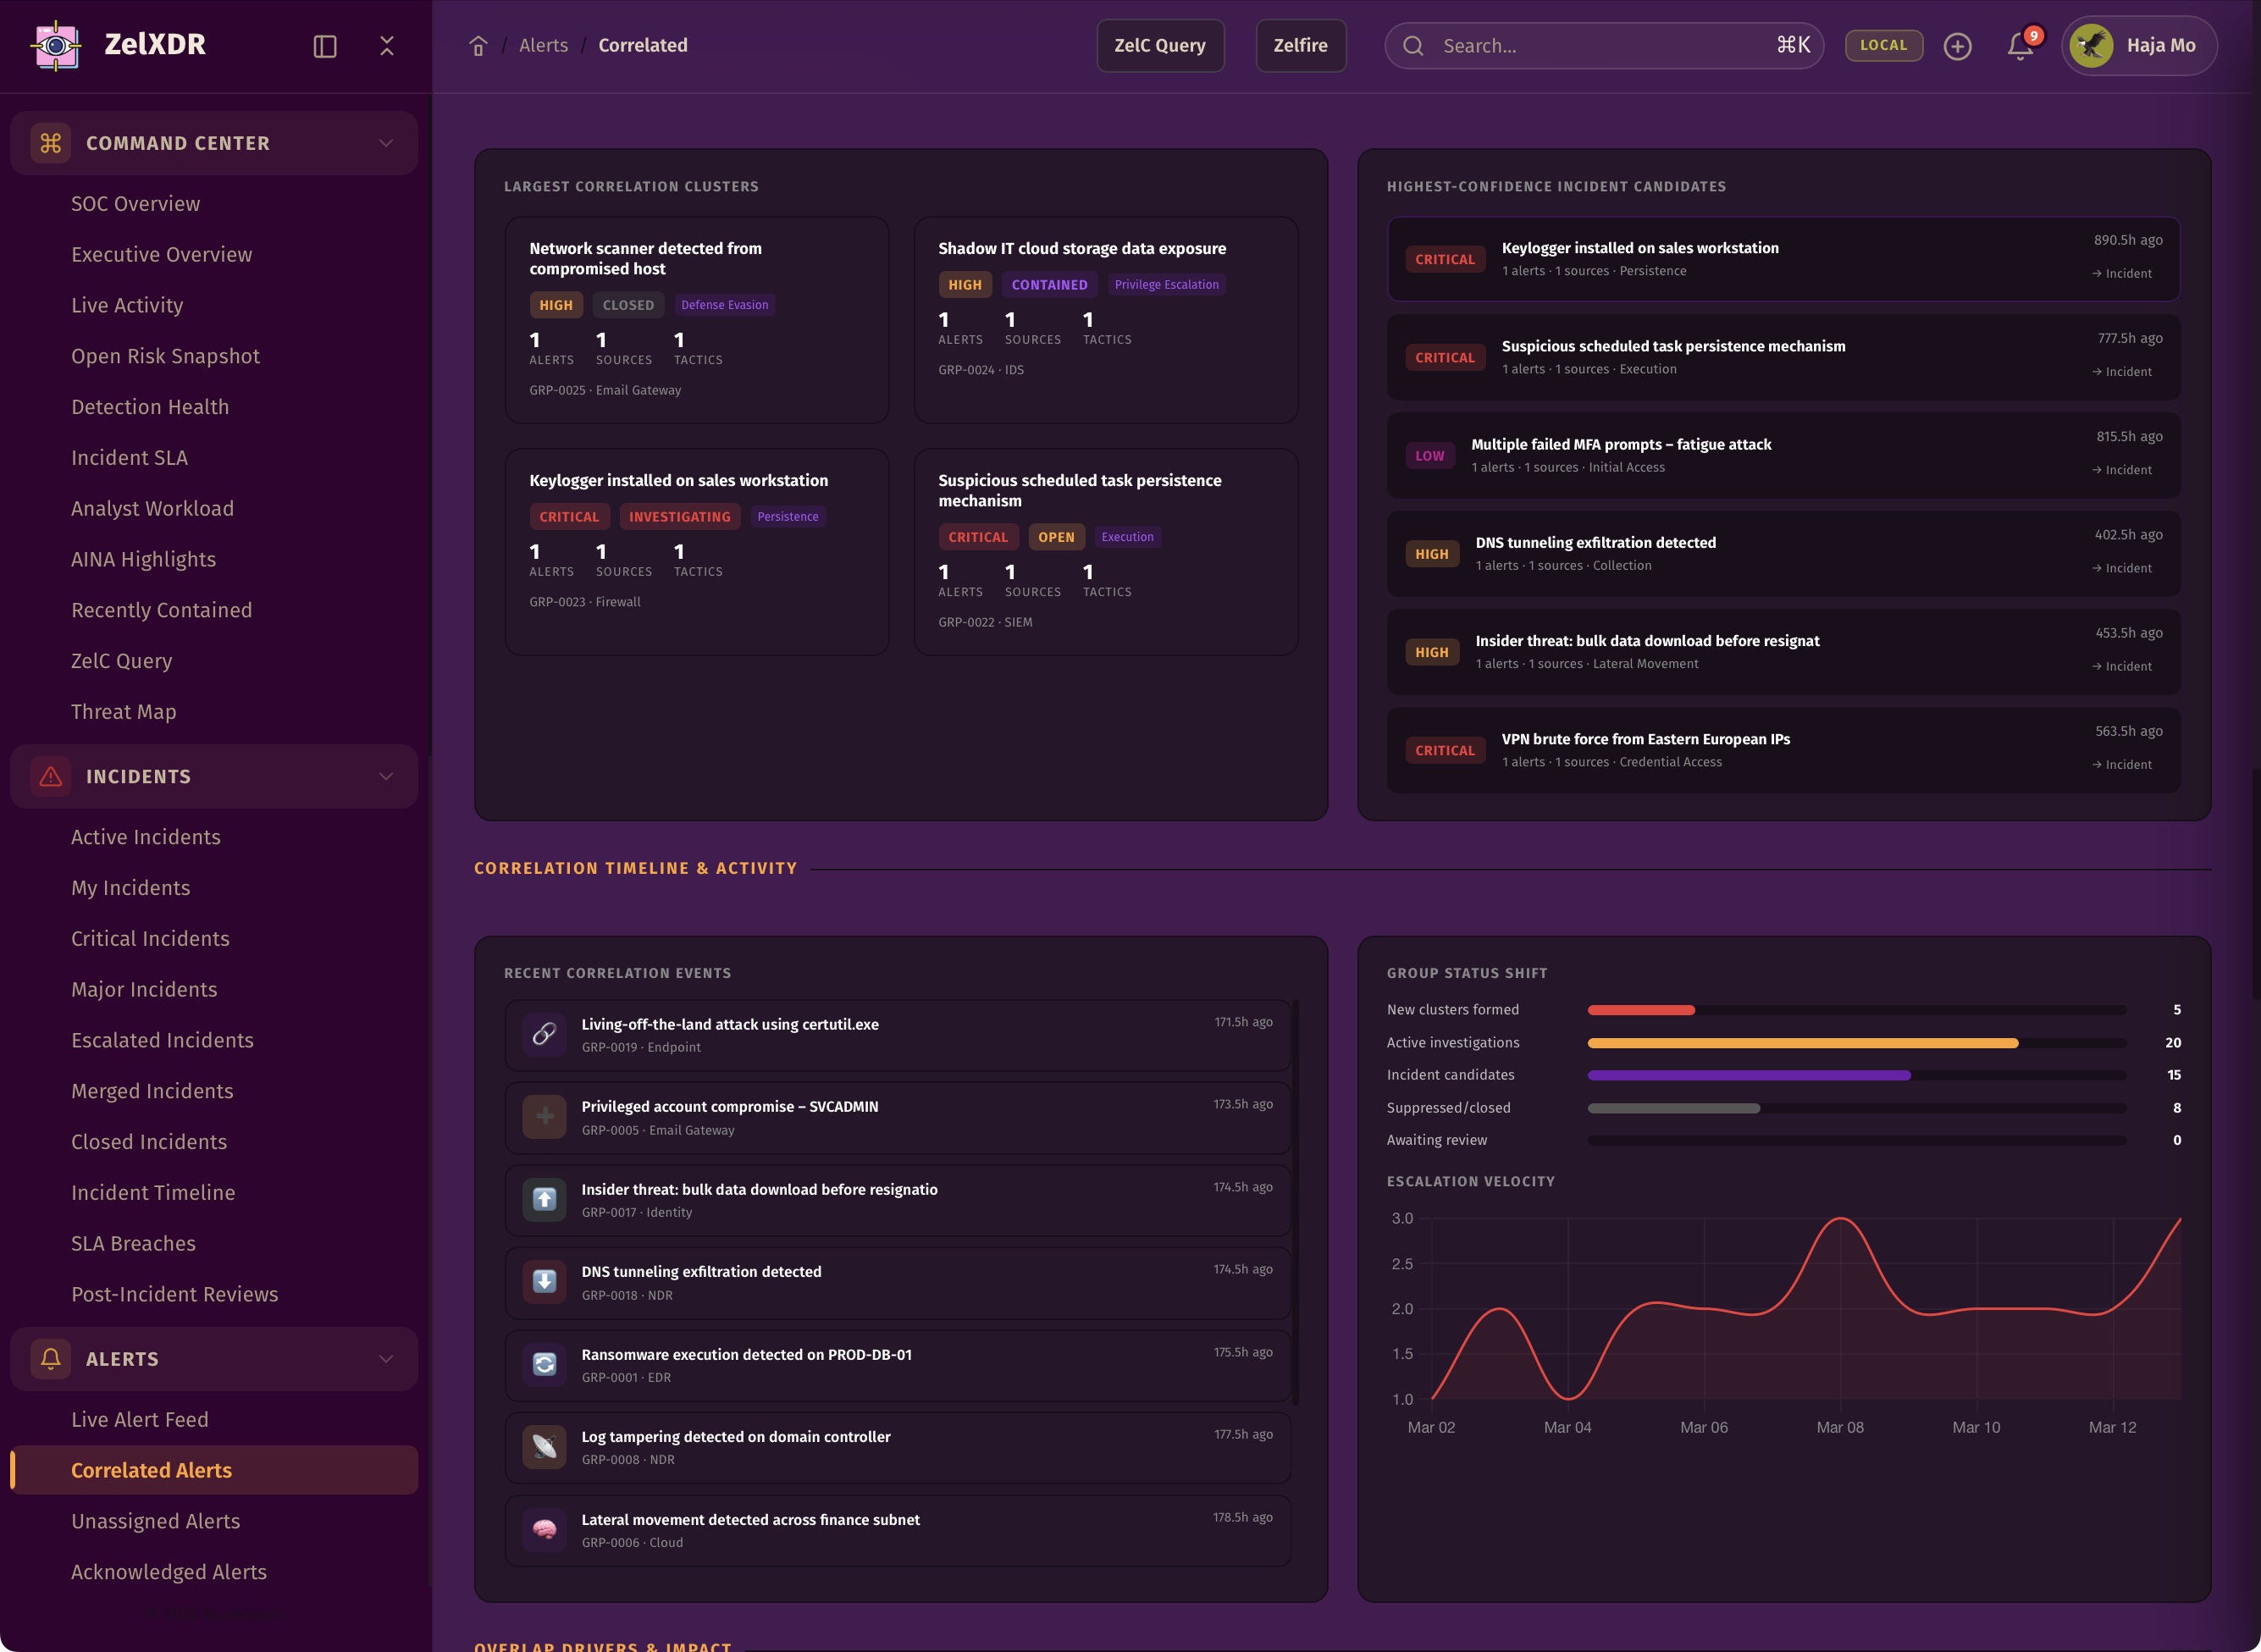
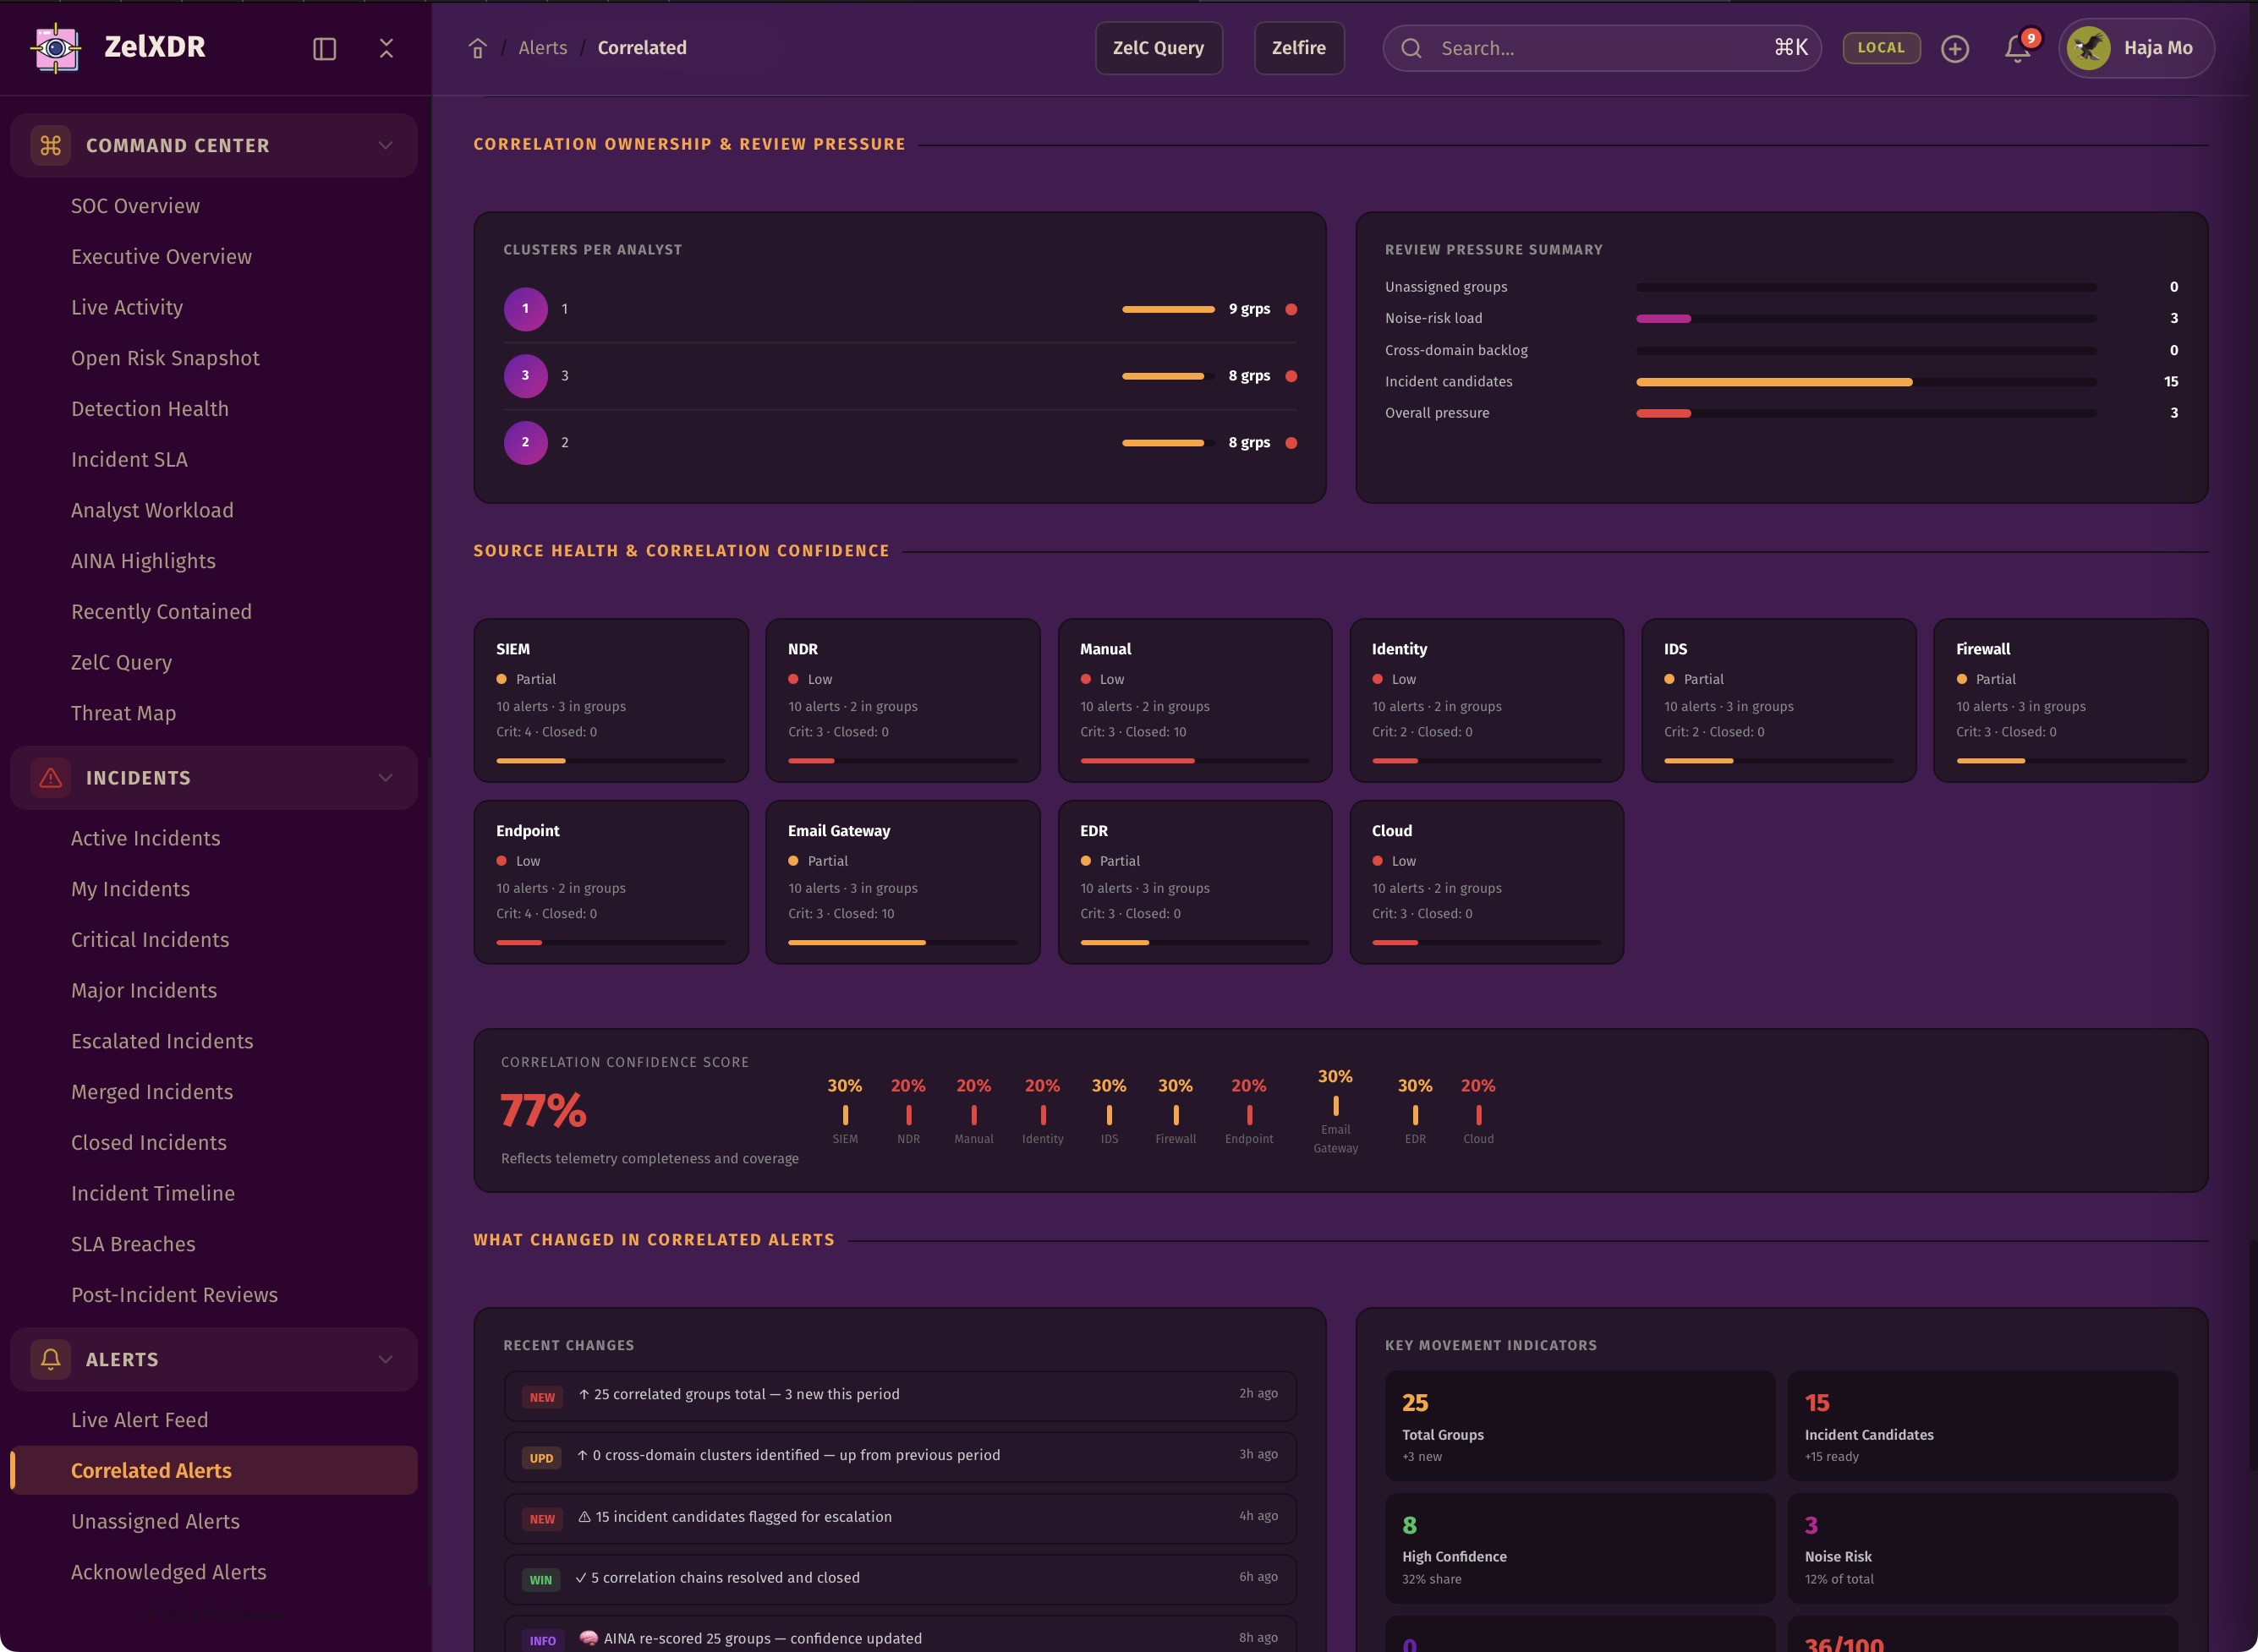
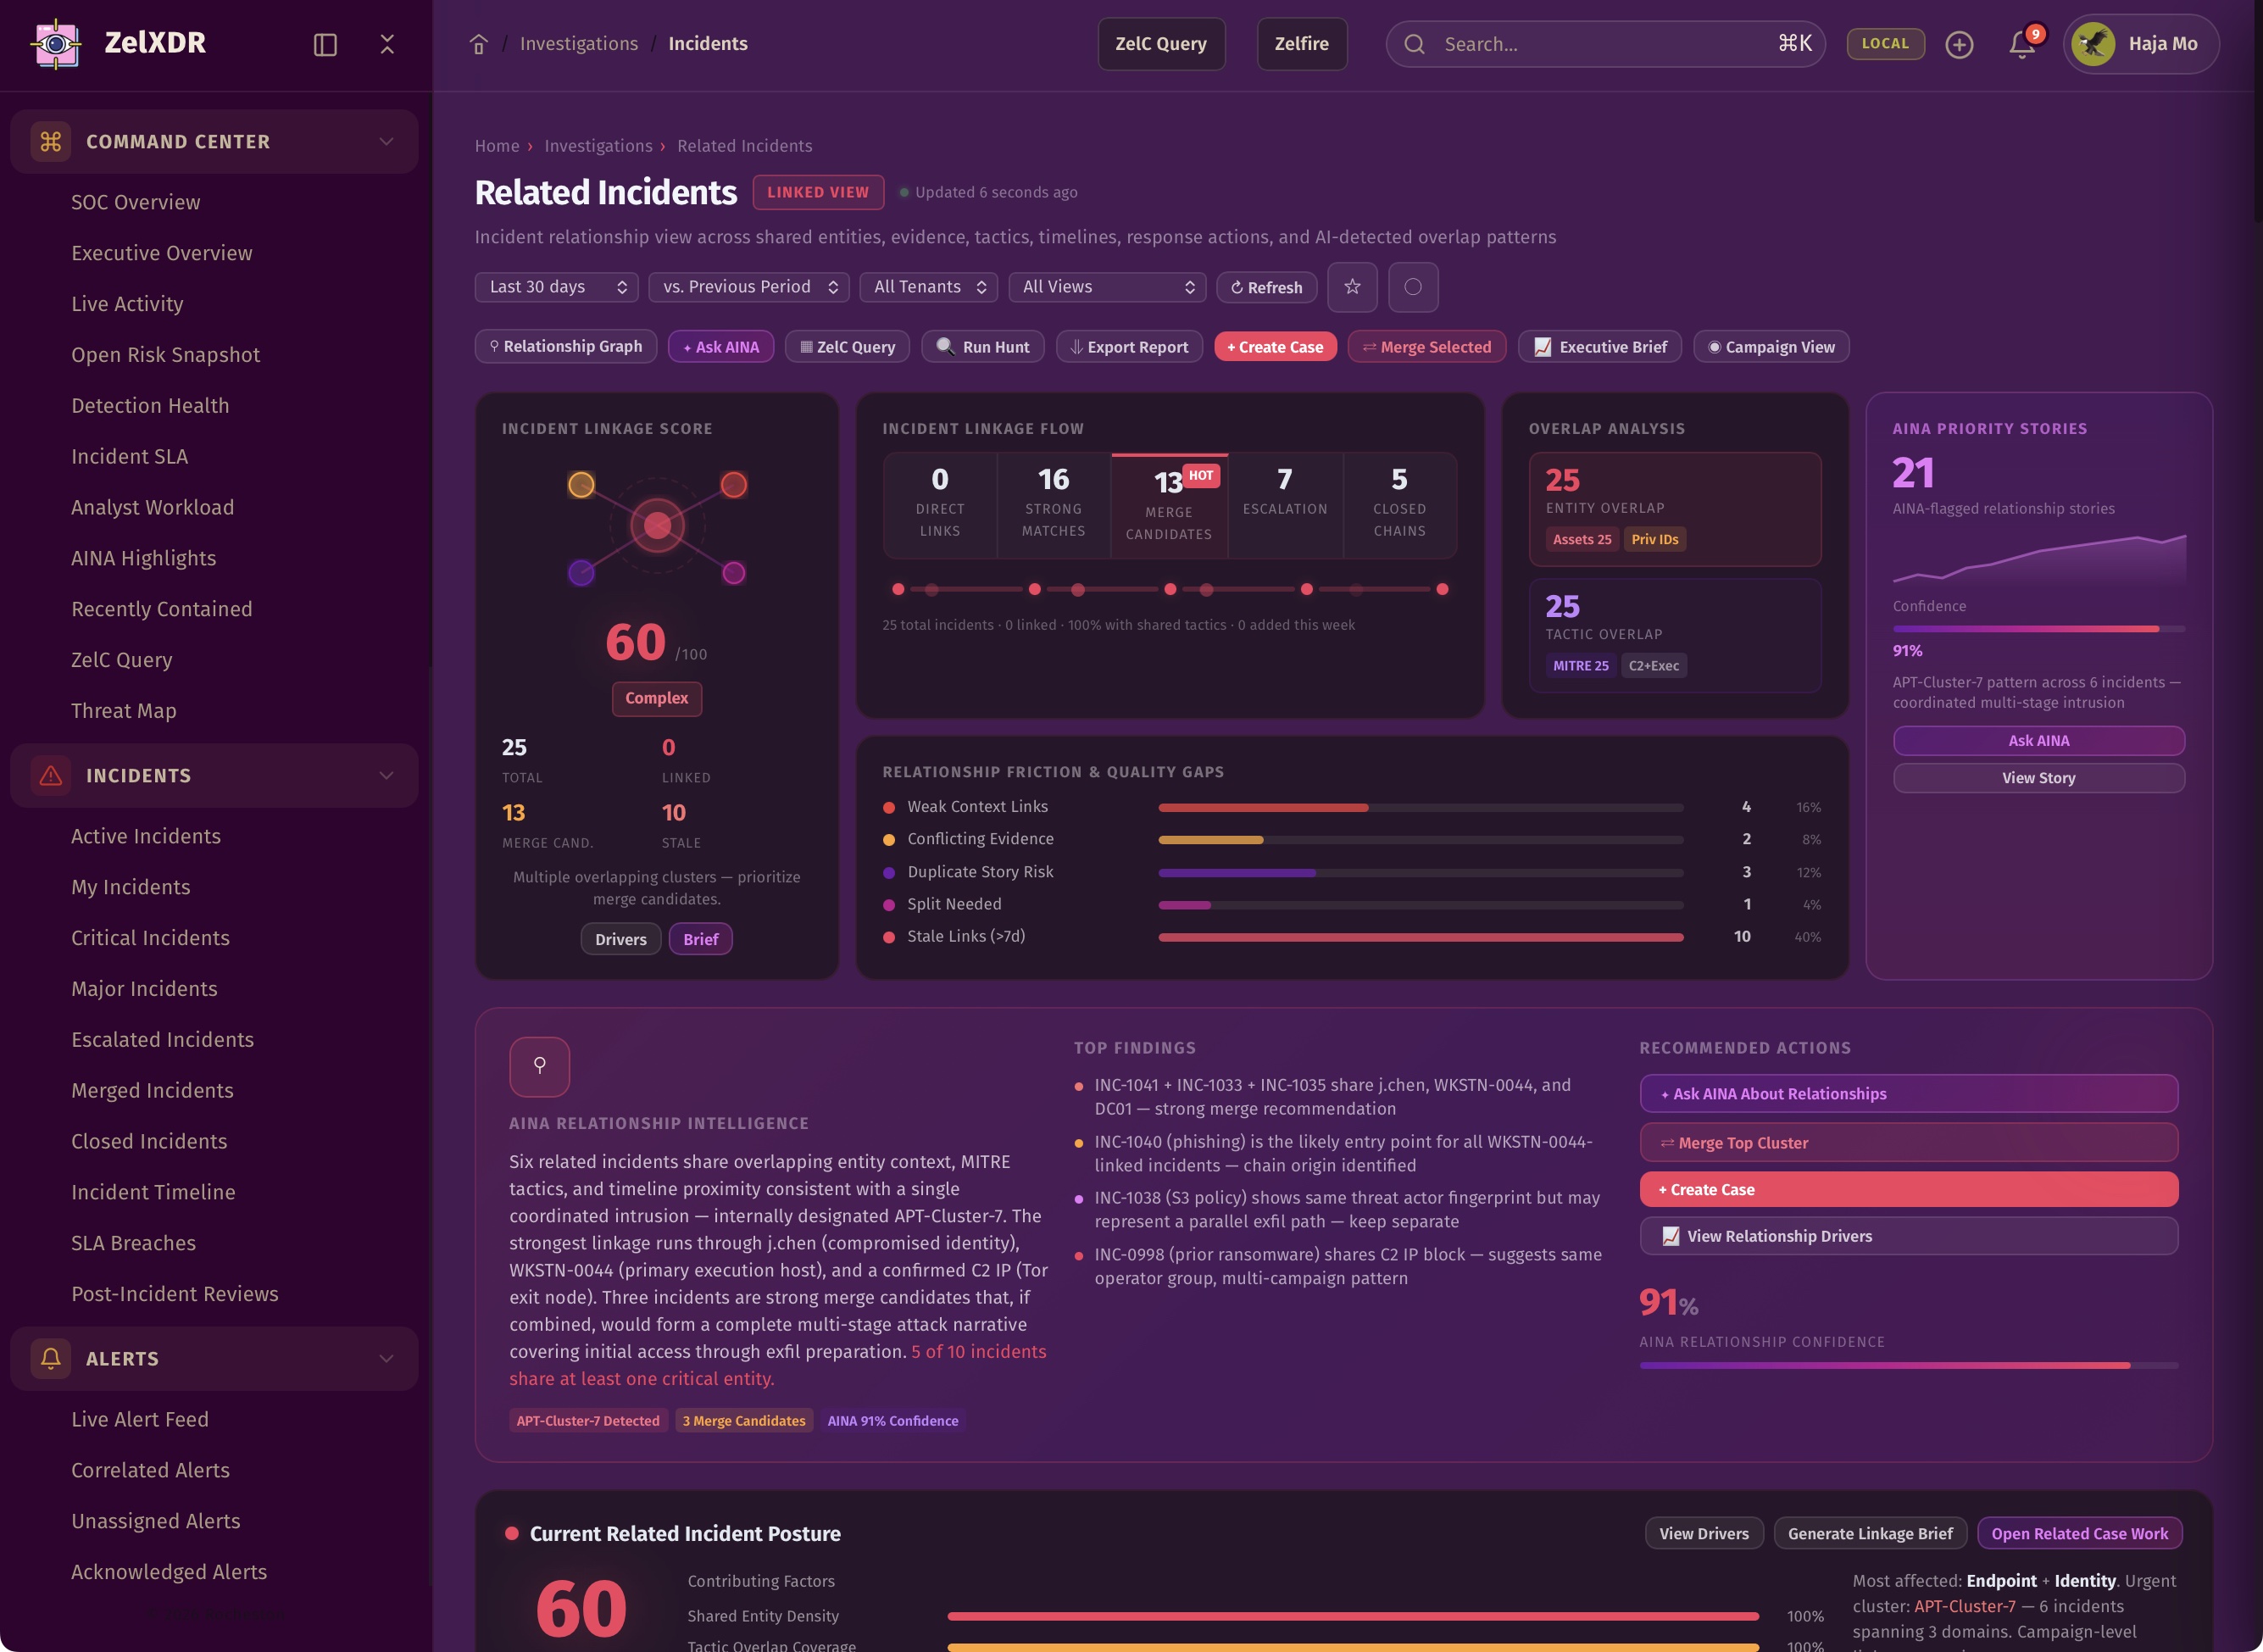
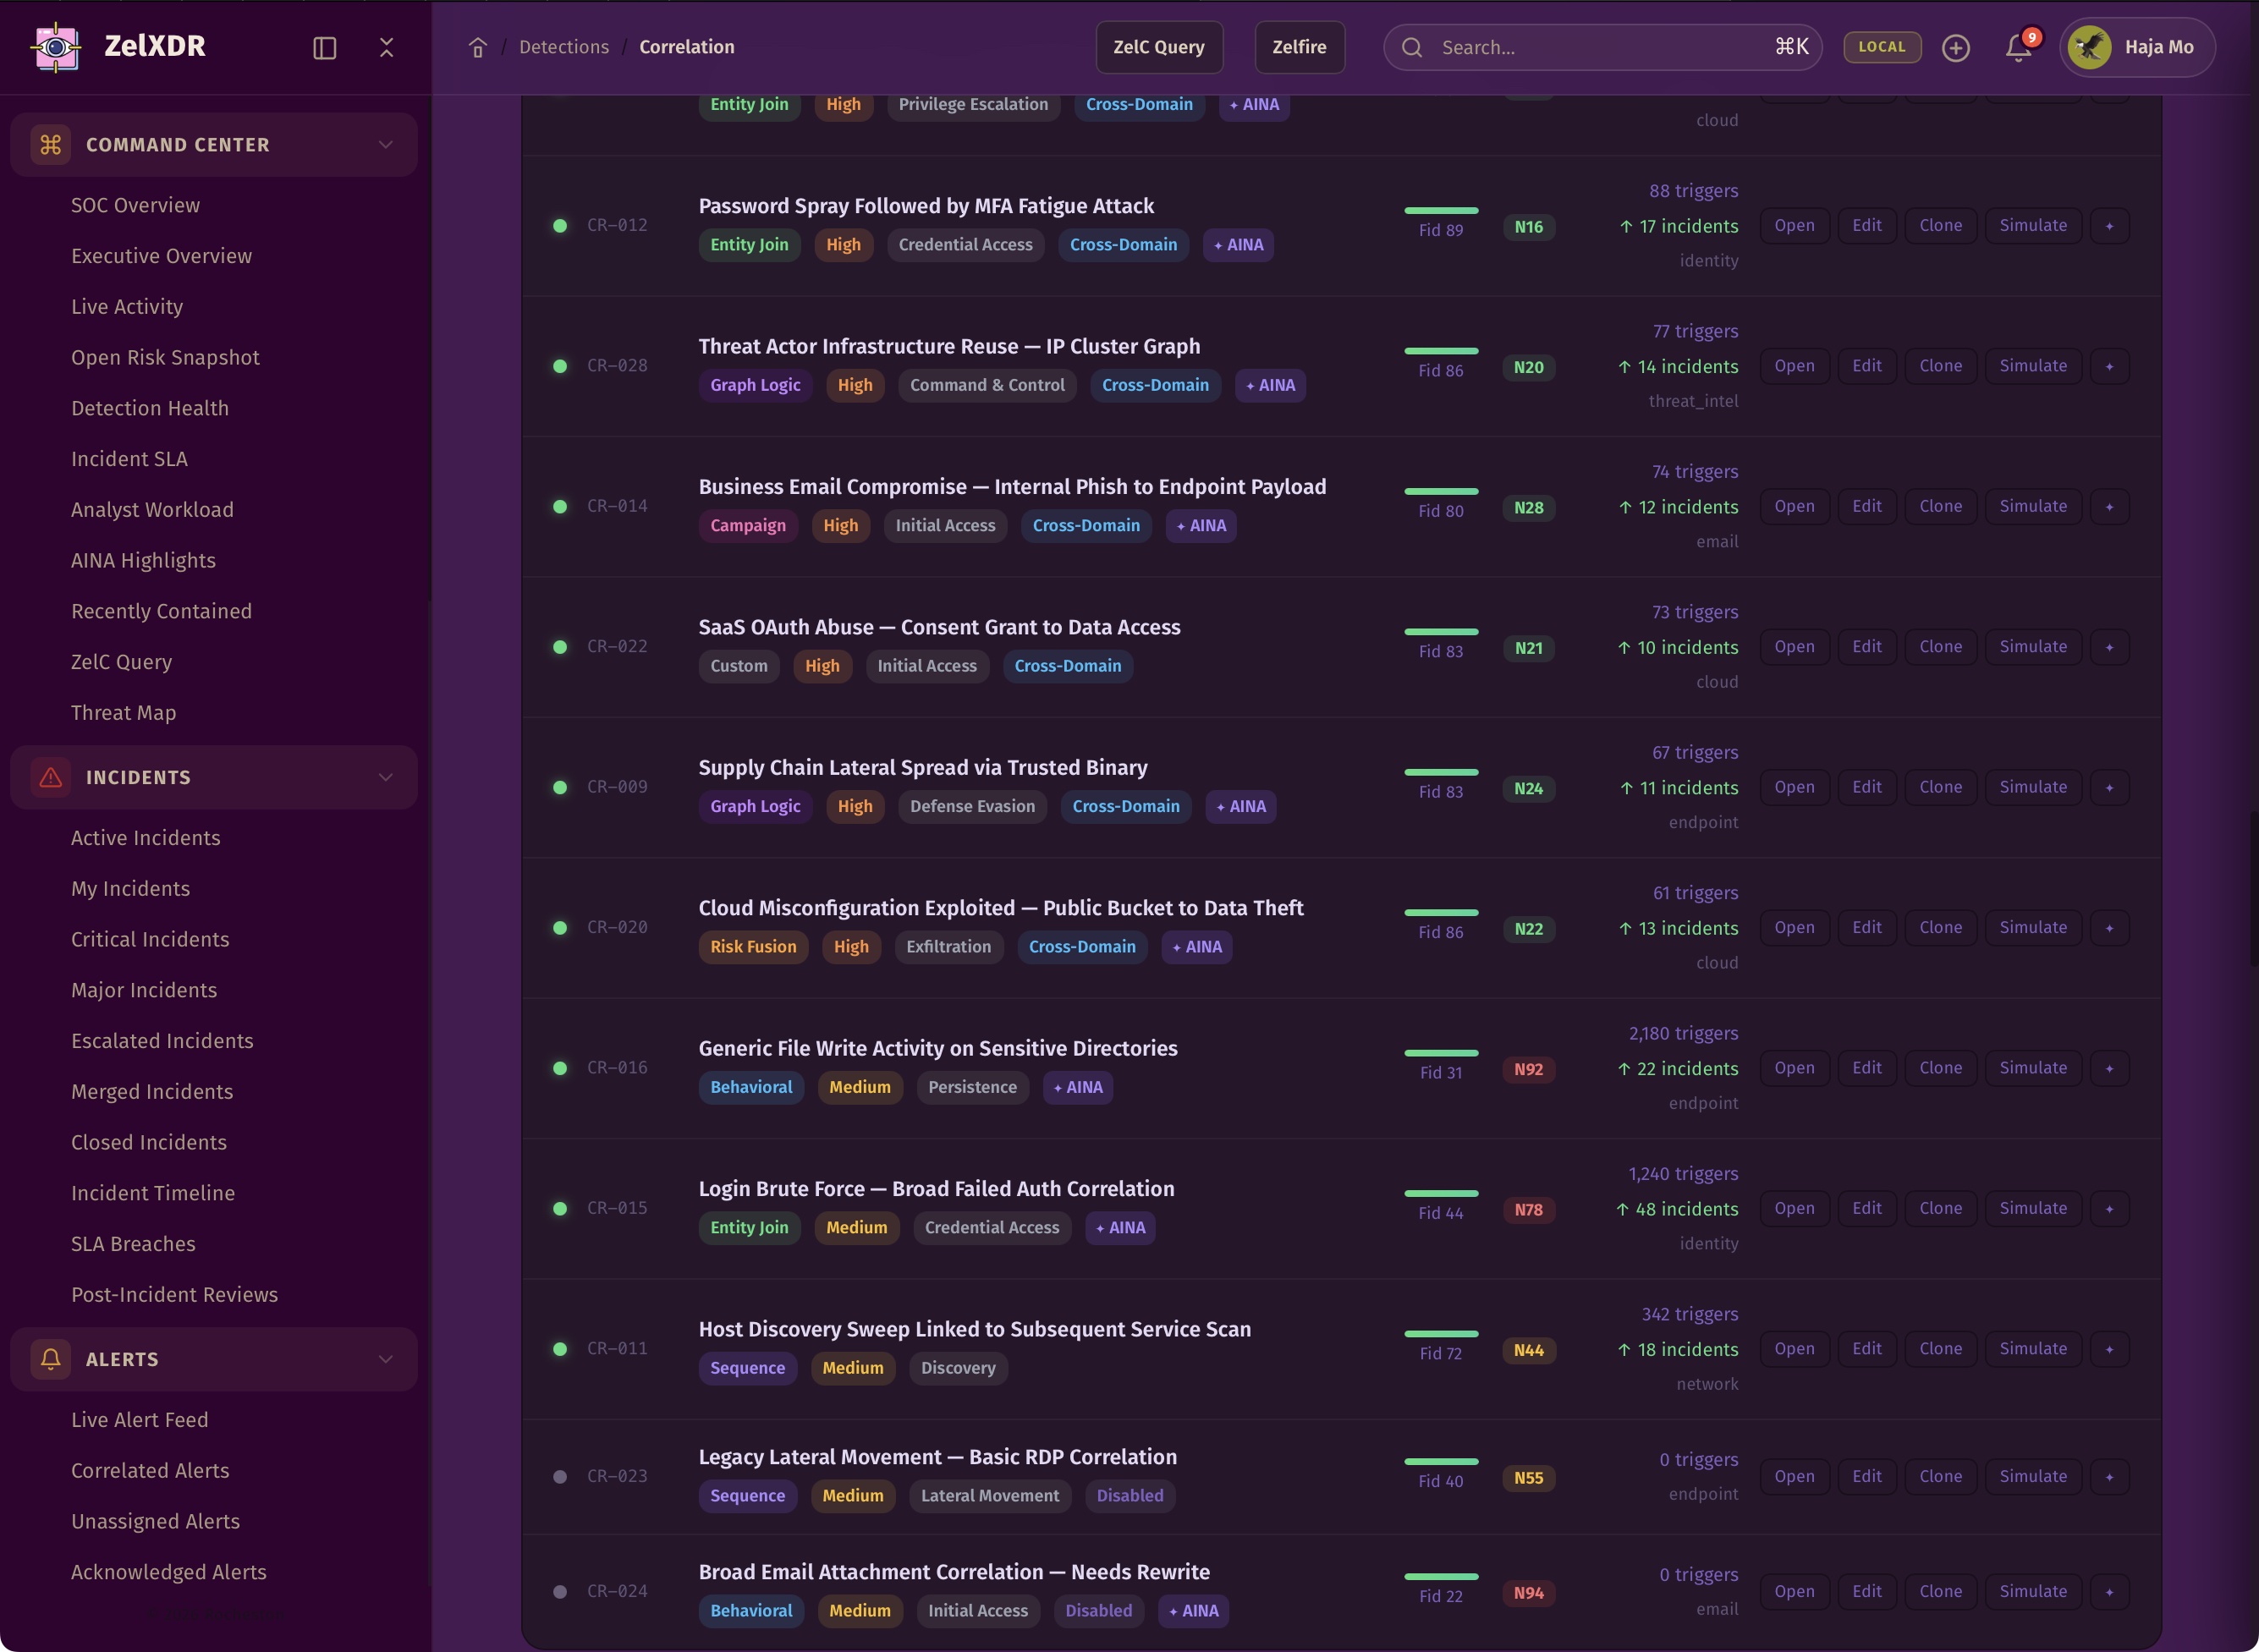
ZelXDR correlates related activity across endpoint, identity, cloud, network, and email so signals become coherent stories instead of isolated technical events.
Correlation is where scattered evidence becomes an attack narrative.
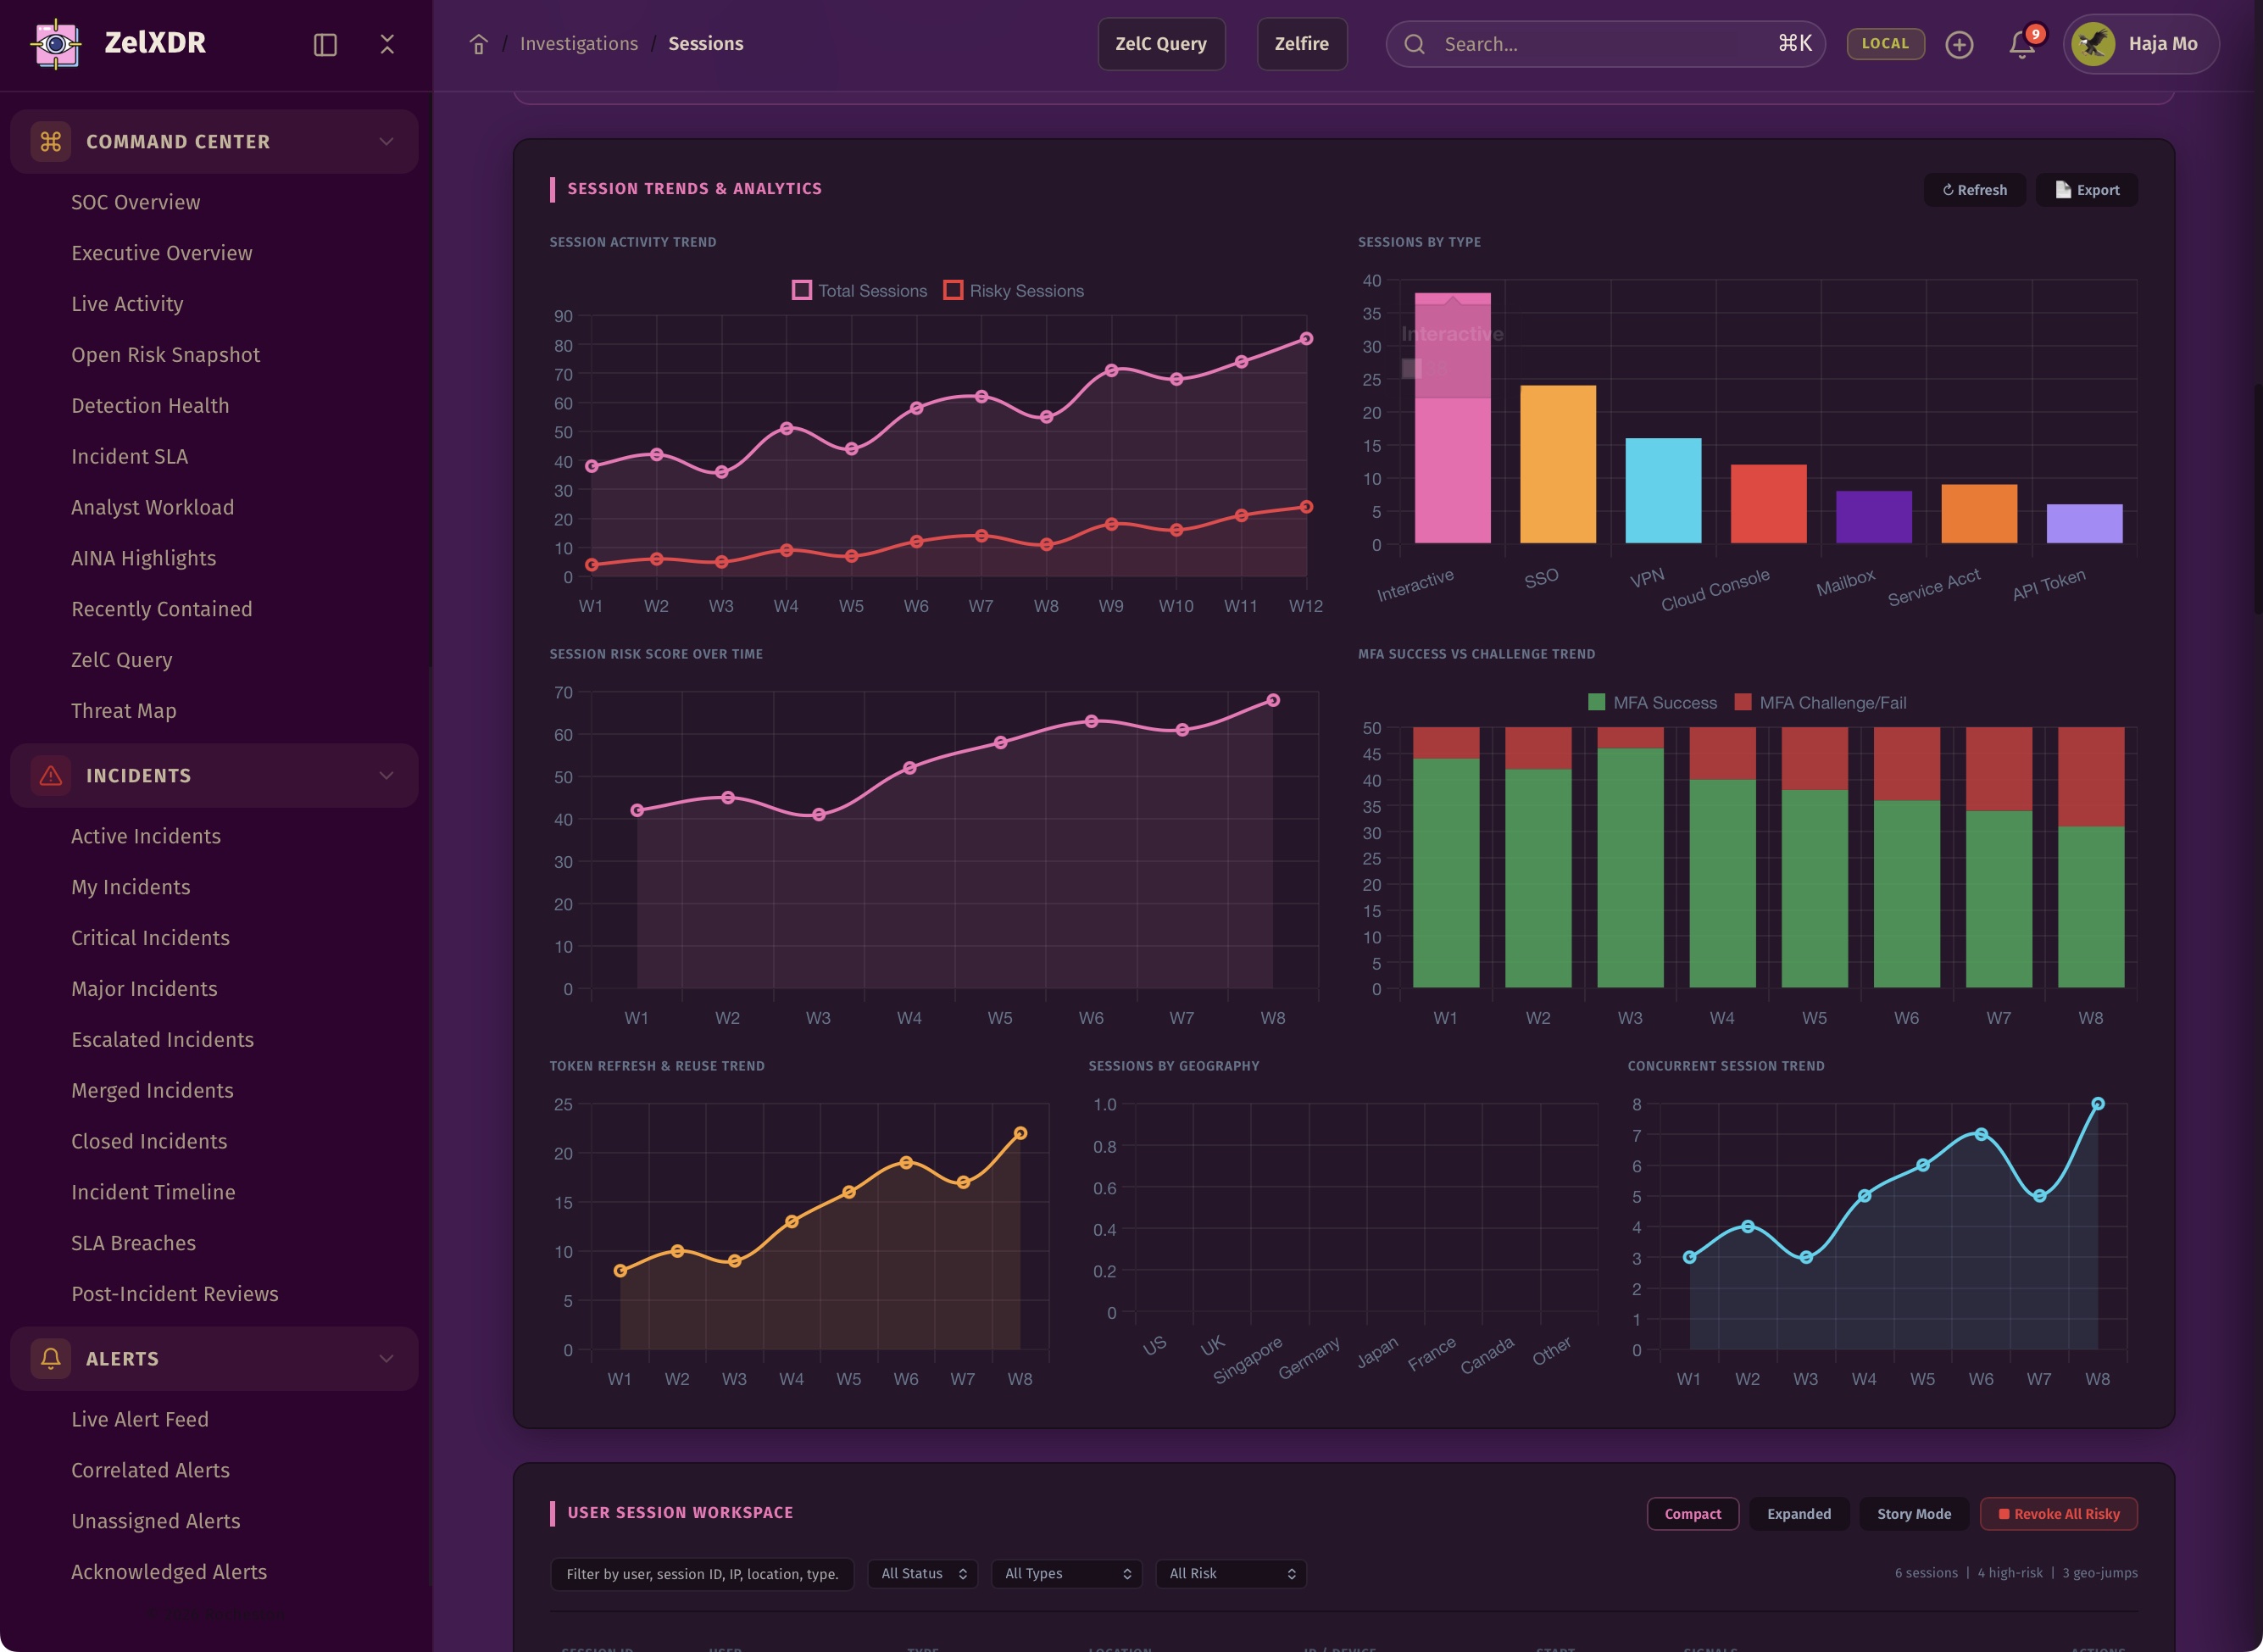
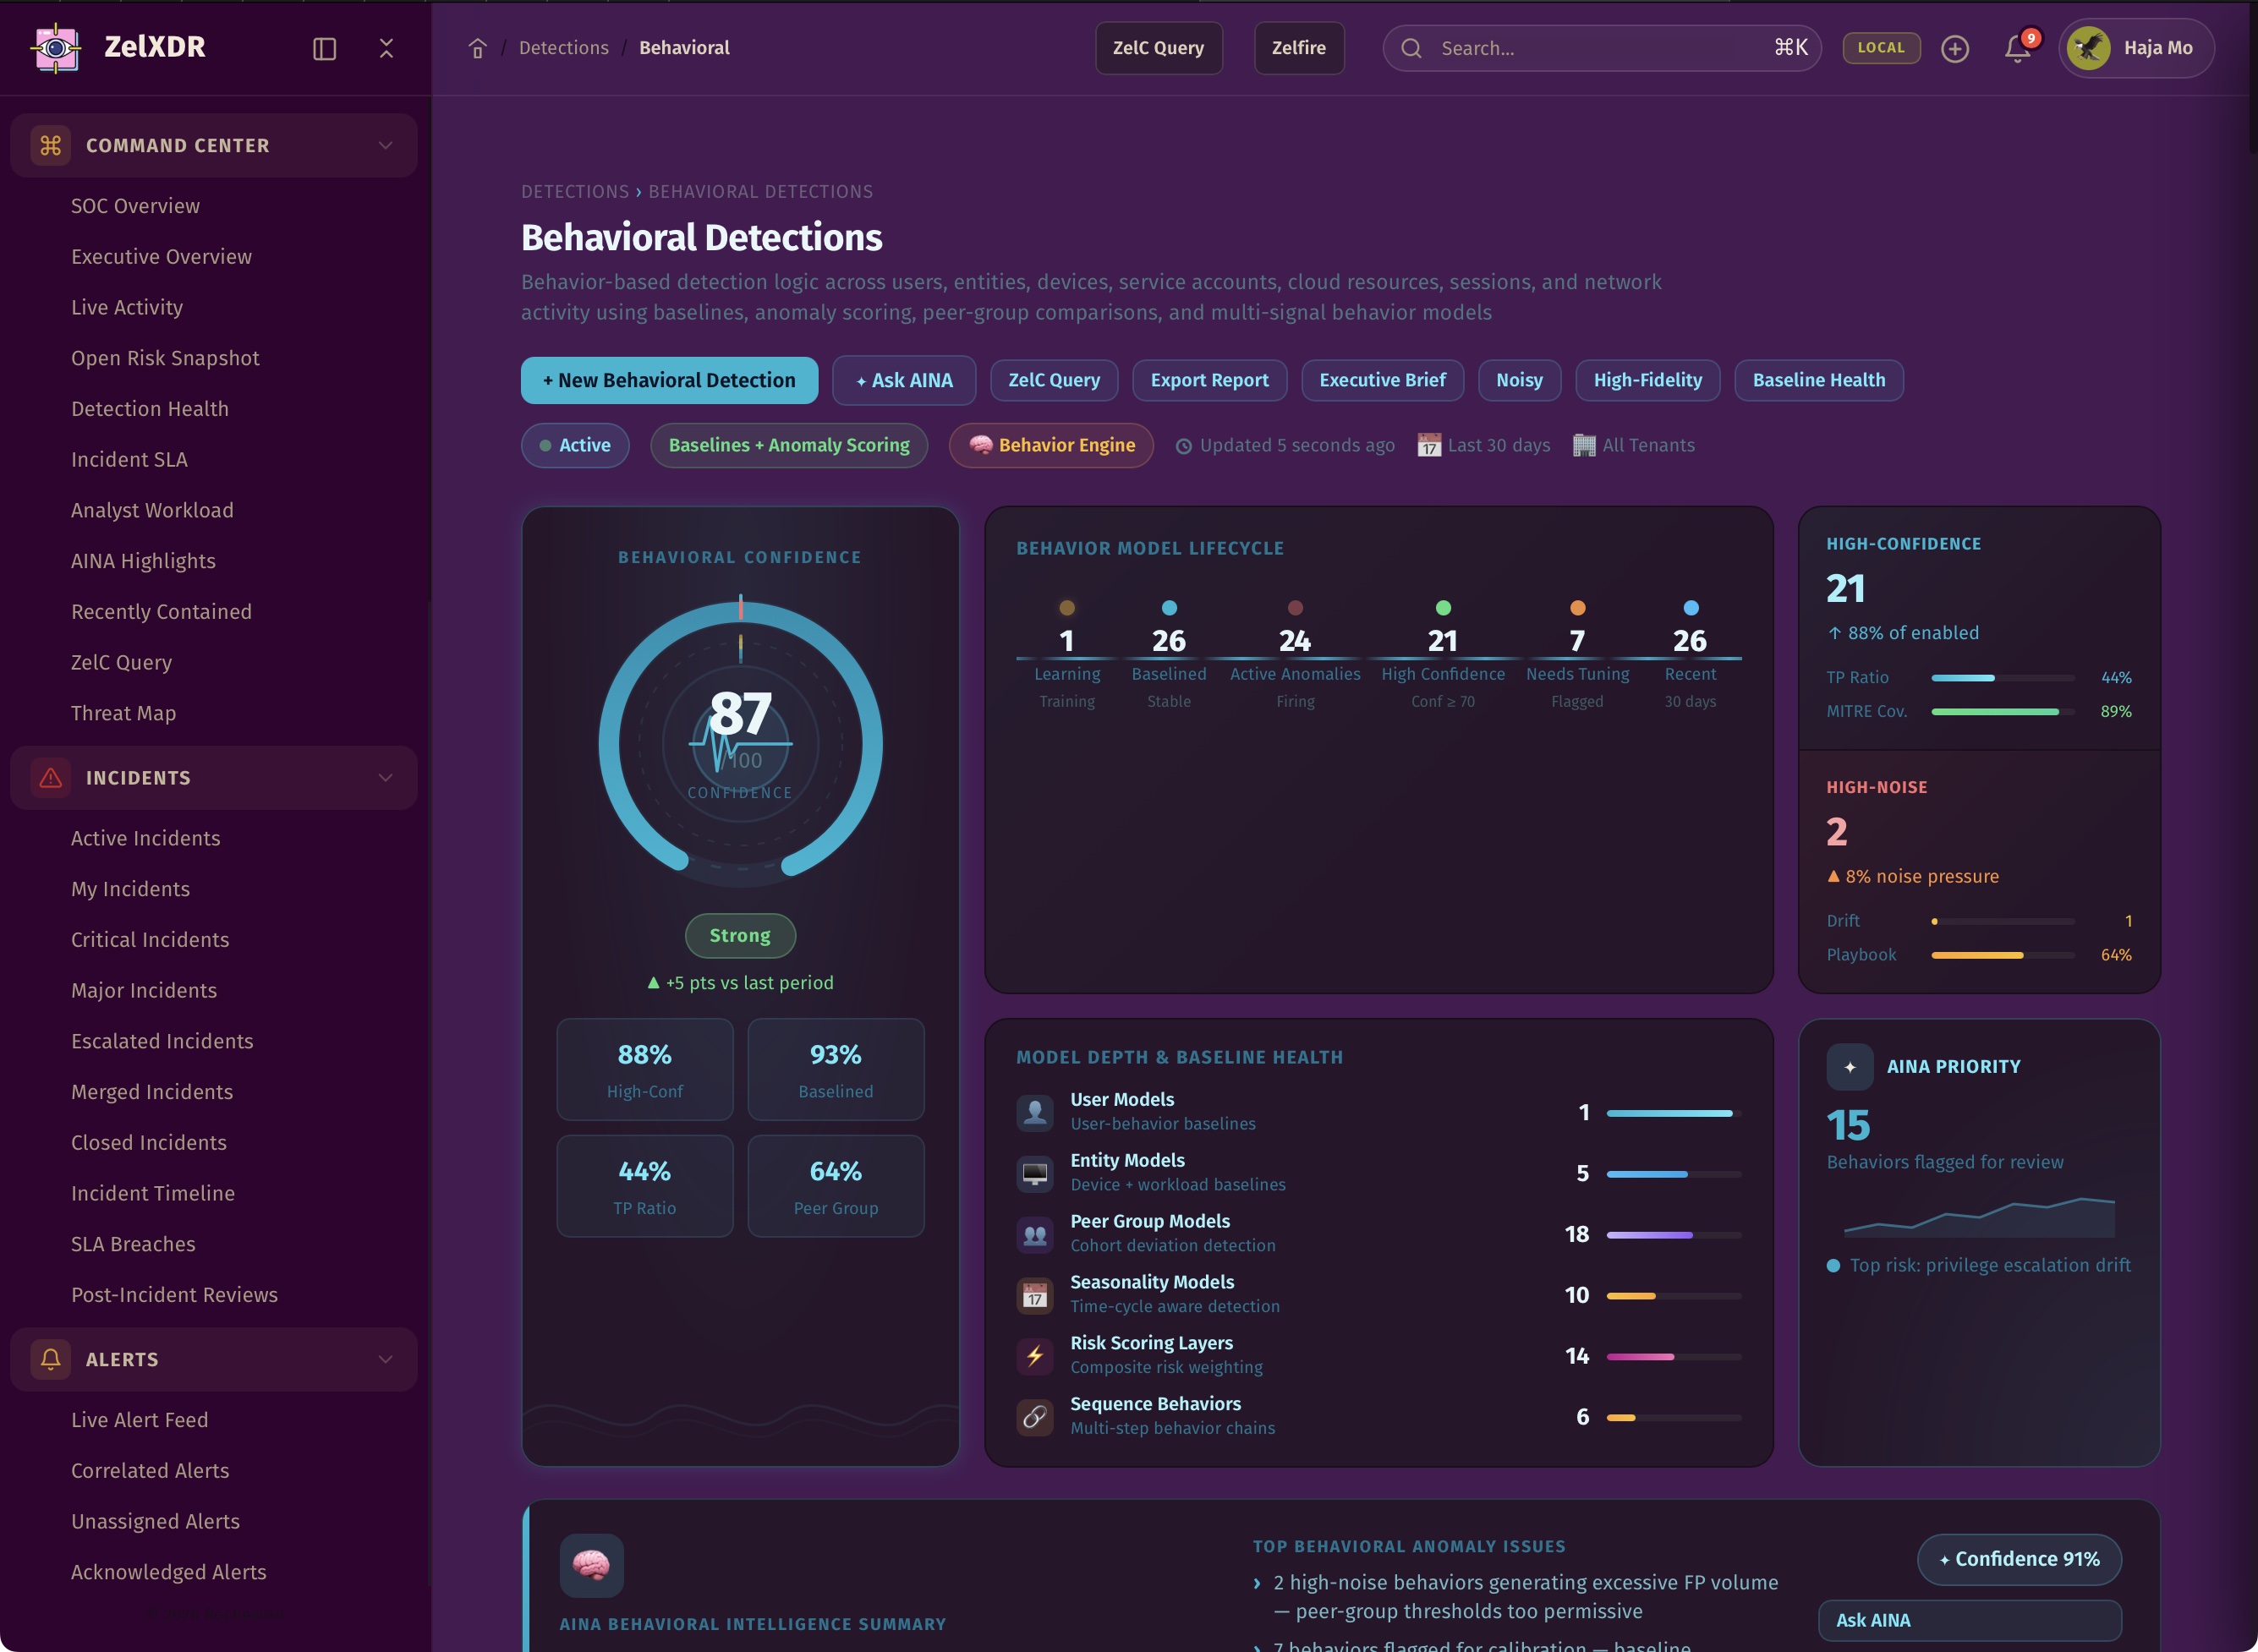
ZelXDR supports user, entity, peer-group, and seasonality-aware behavioral detections that reveal suspicious deviations with more precision than static logic alone.
Patterns reveal intent long before labels do.
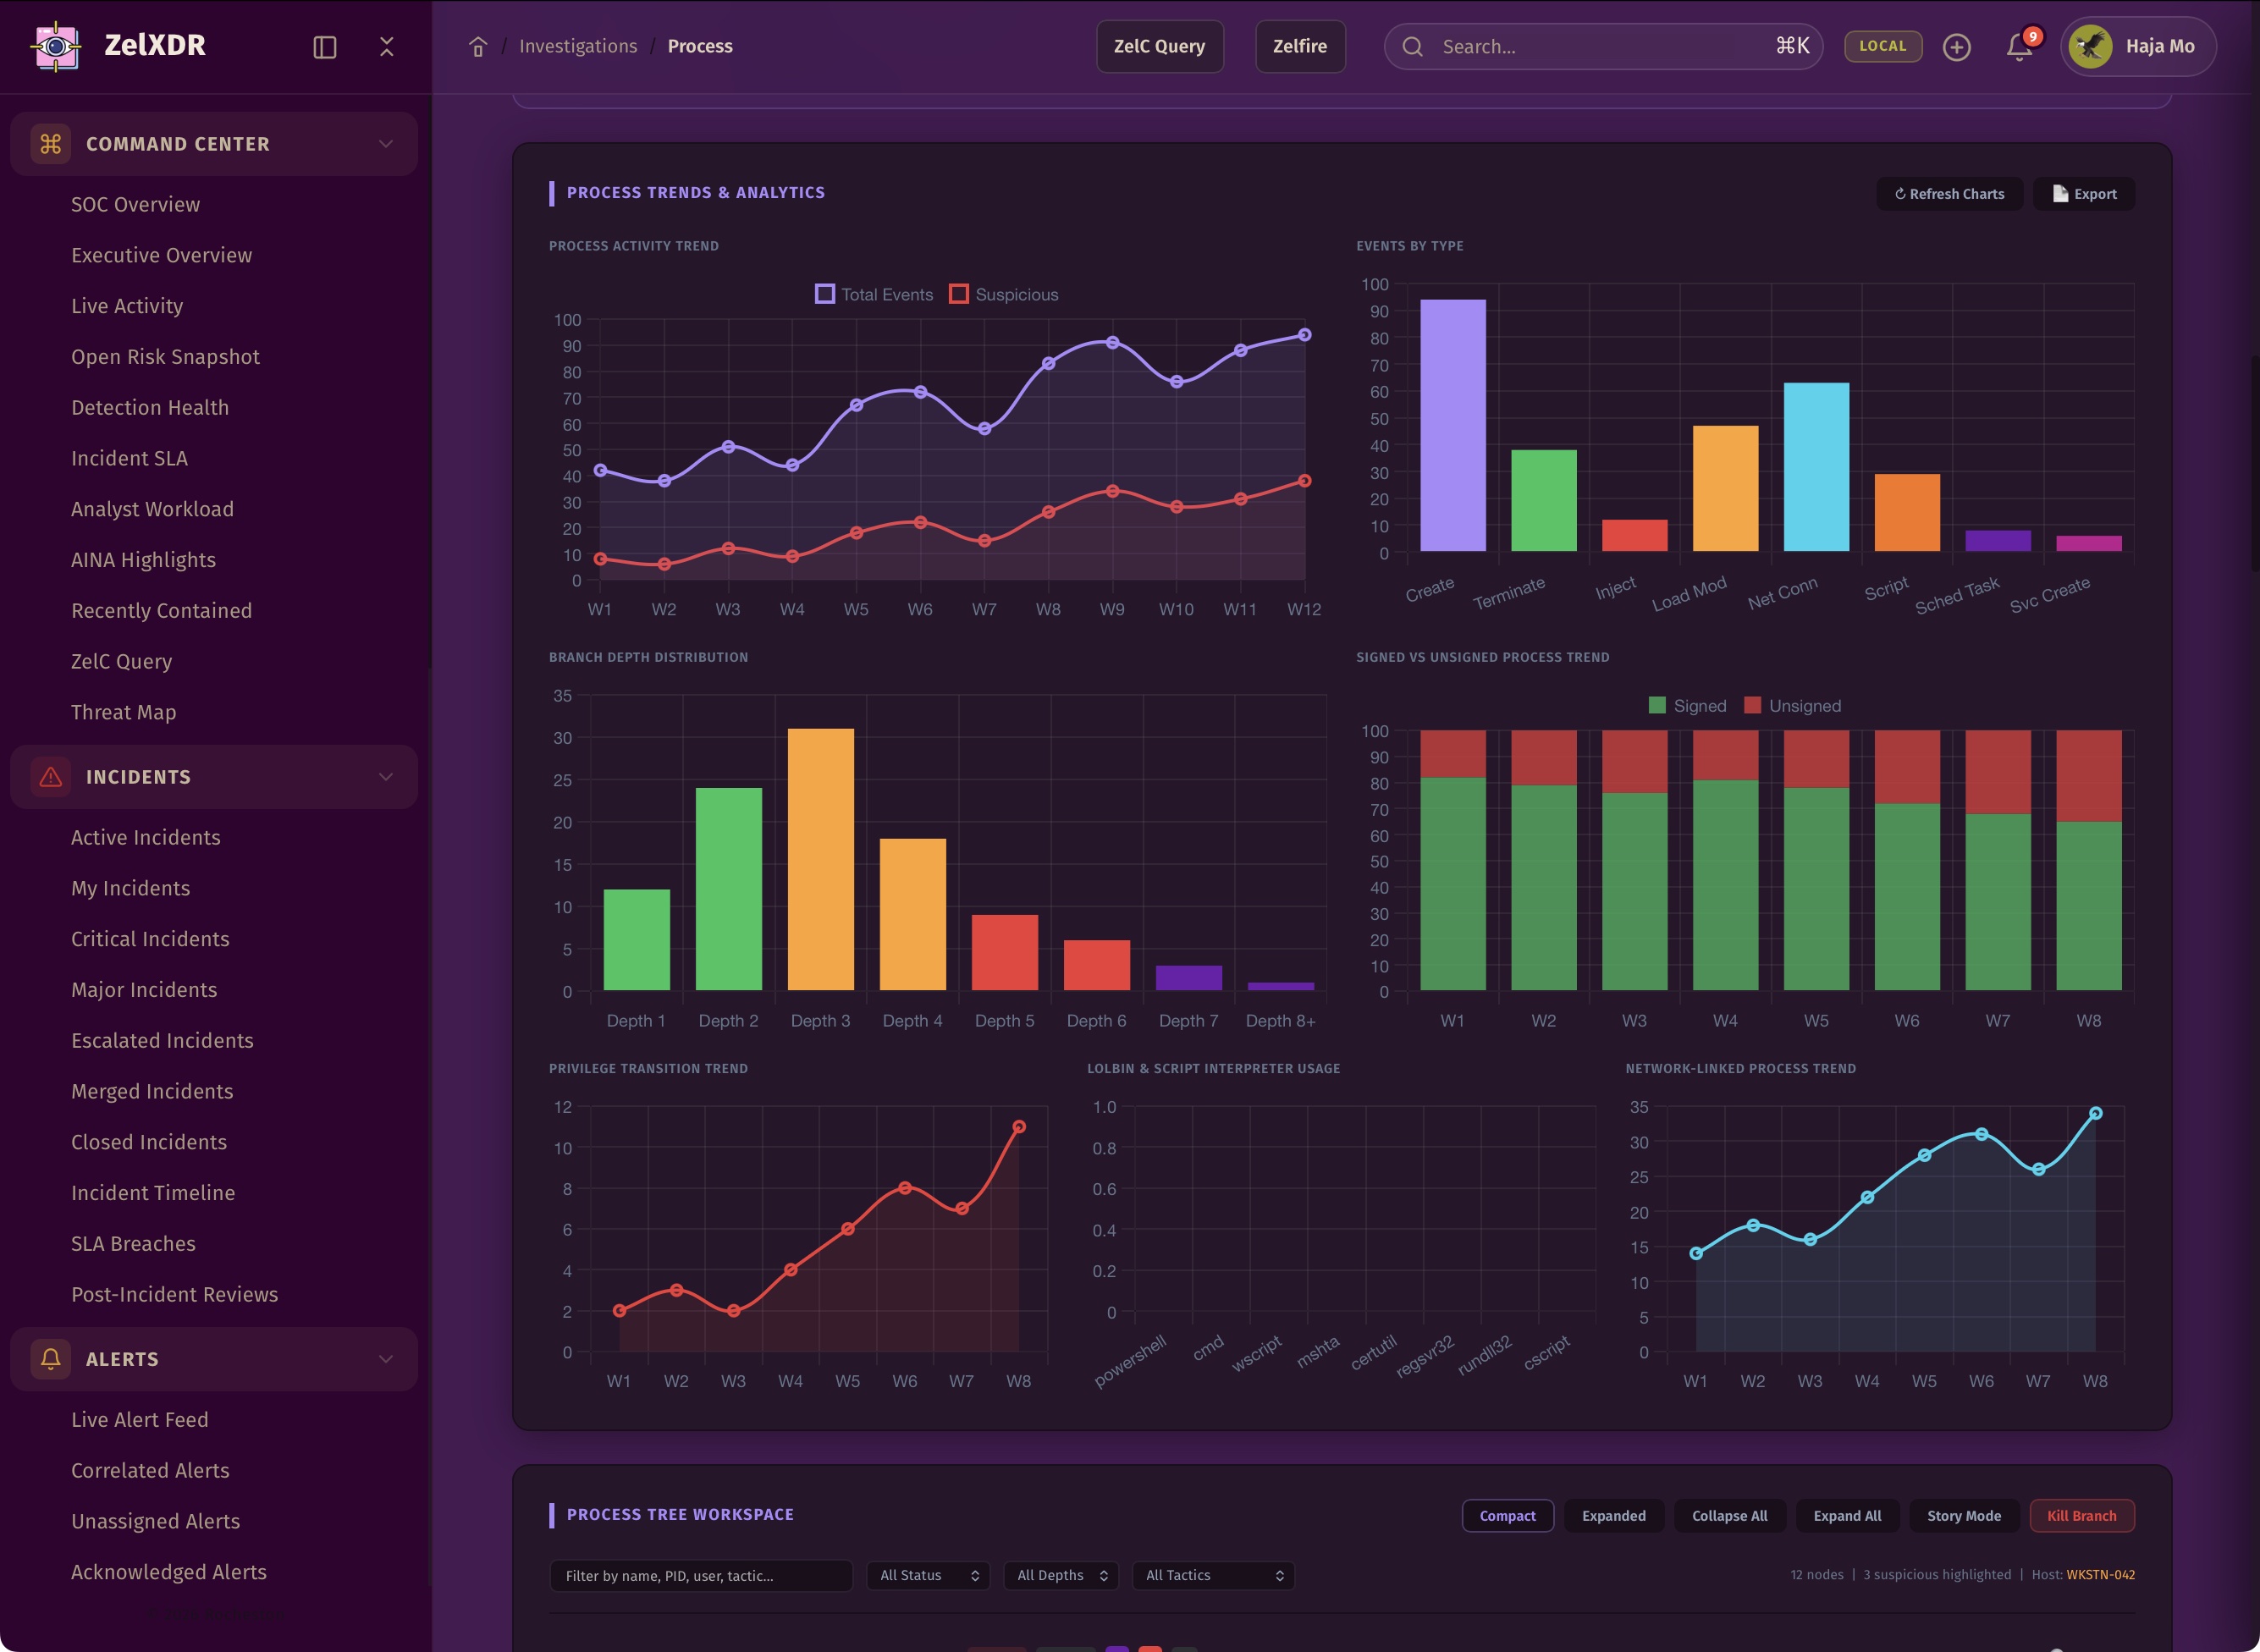
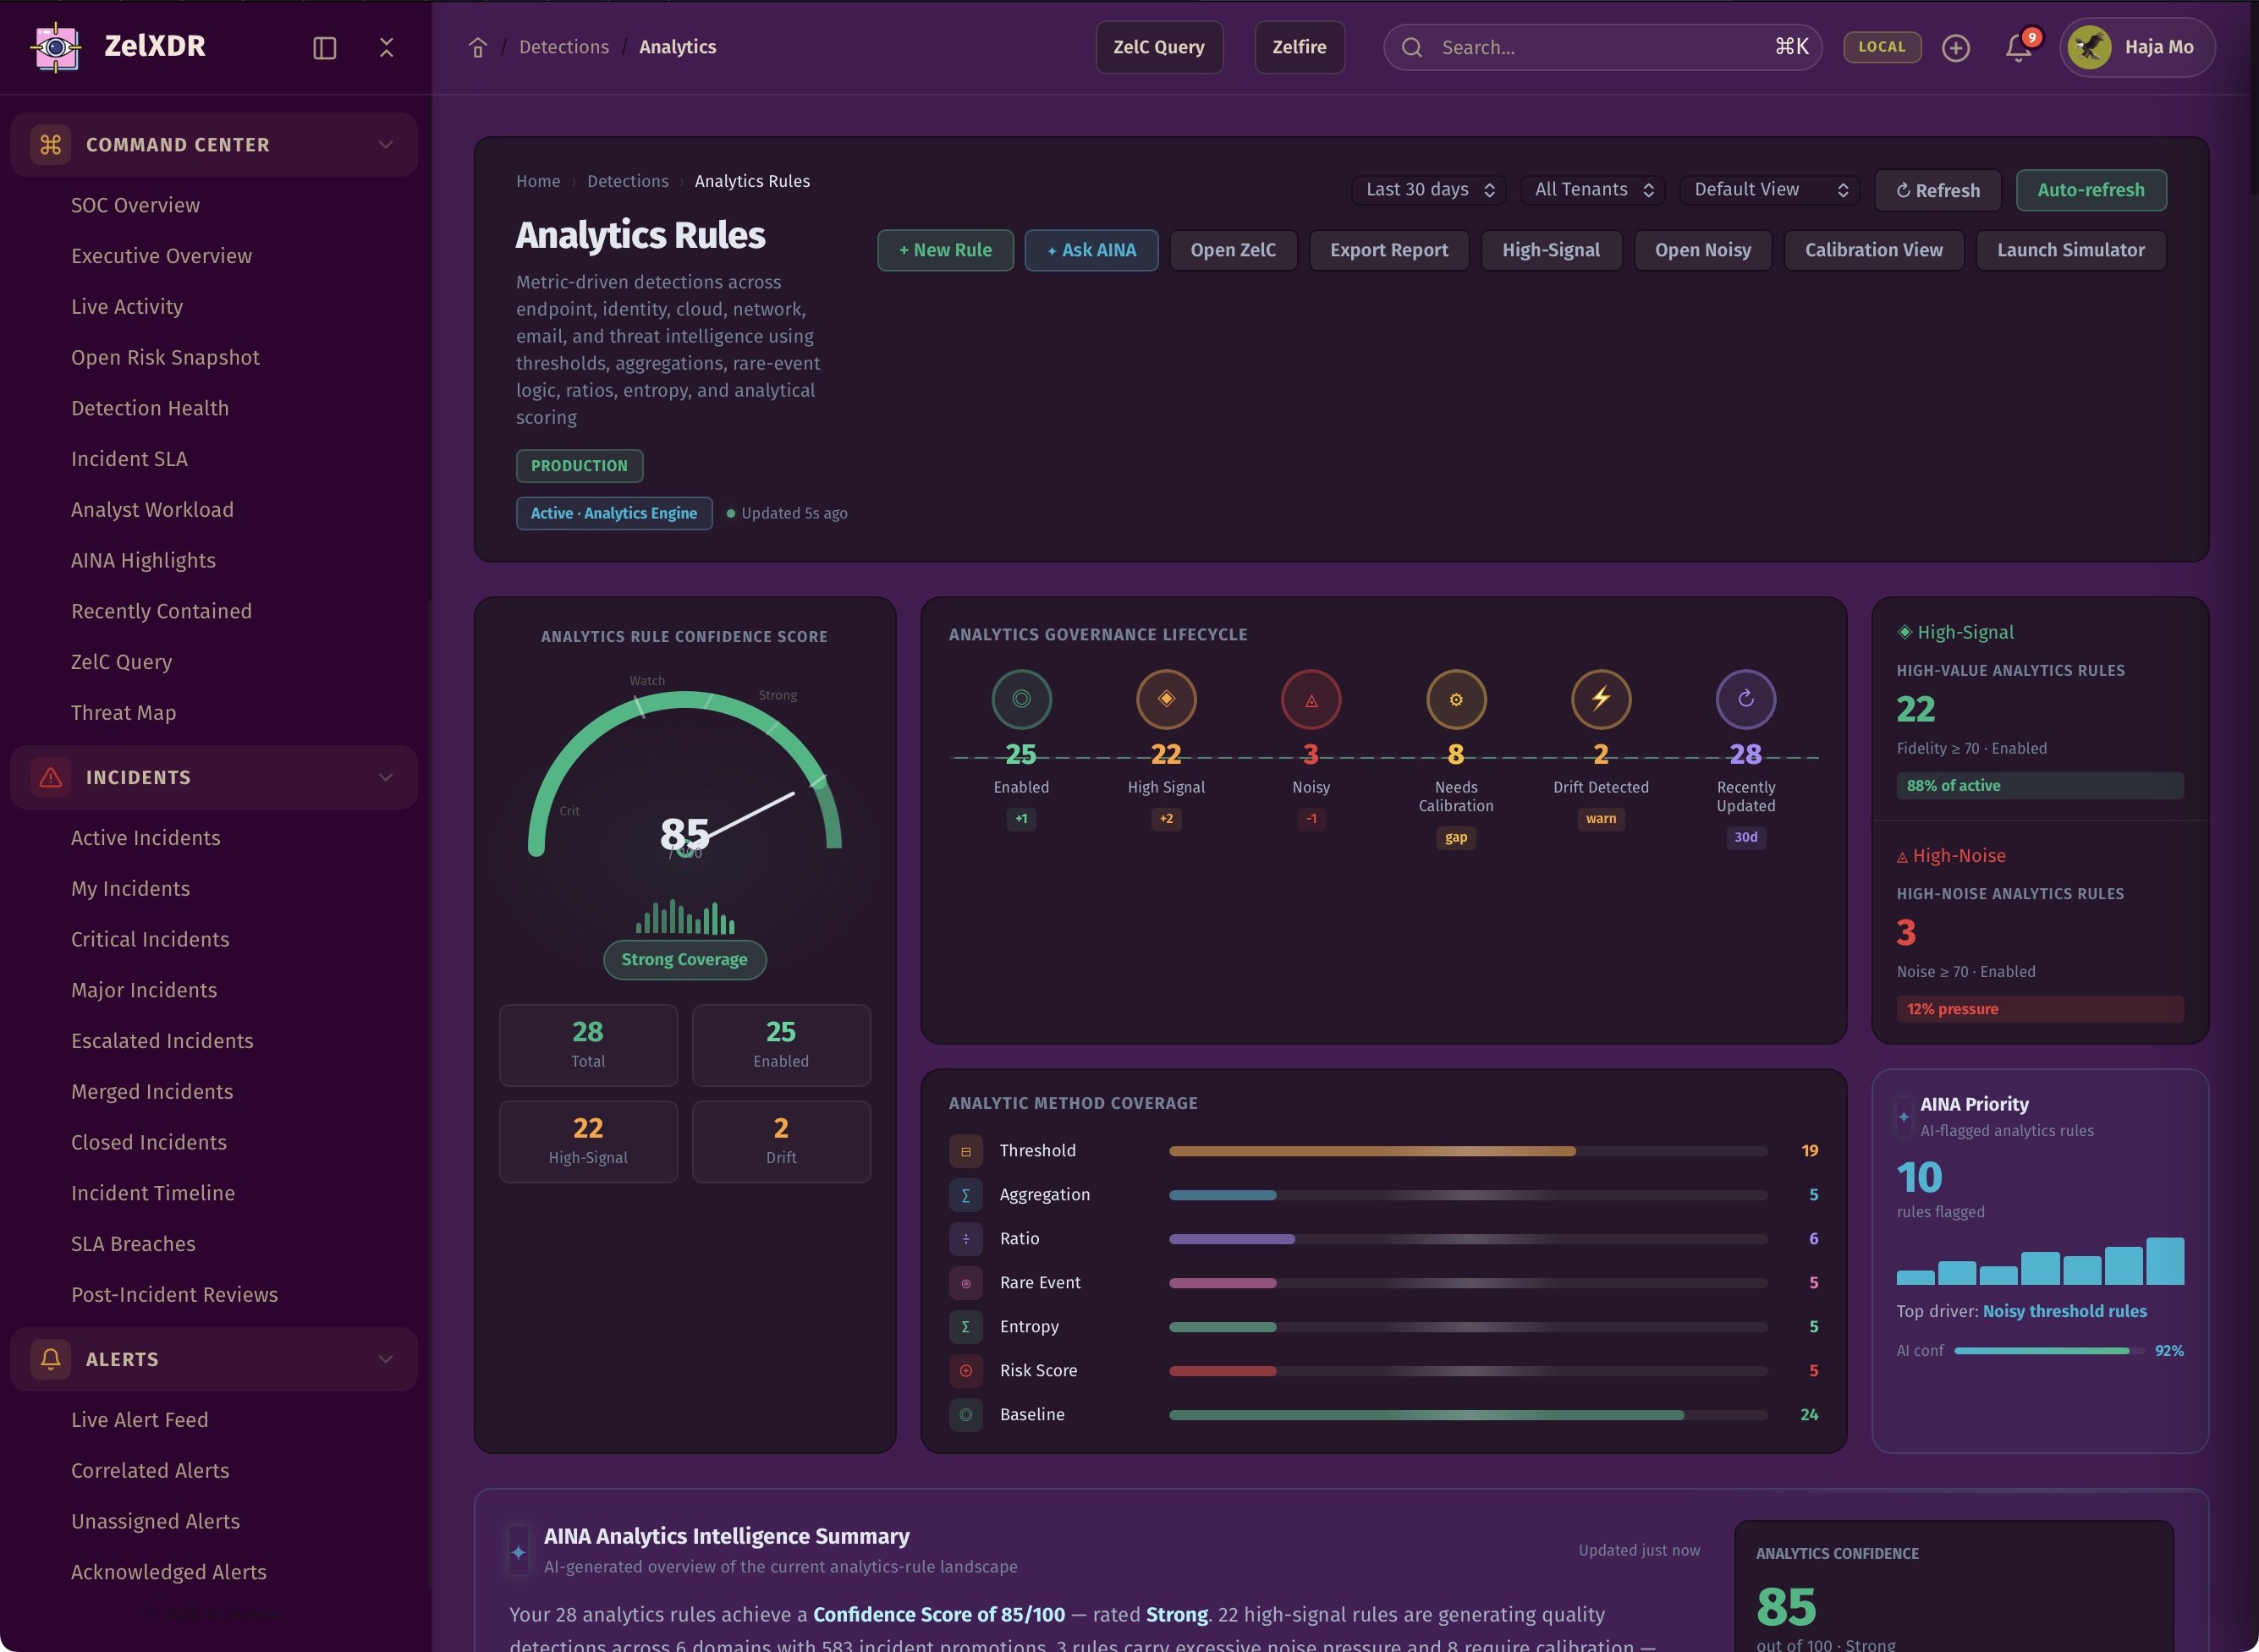
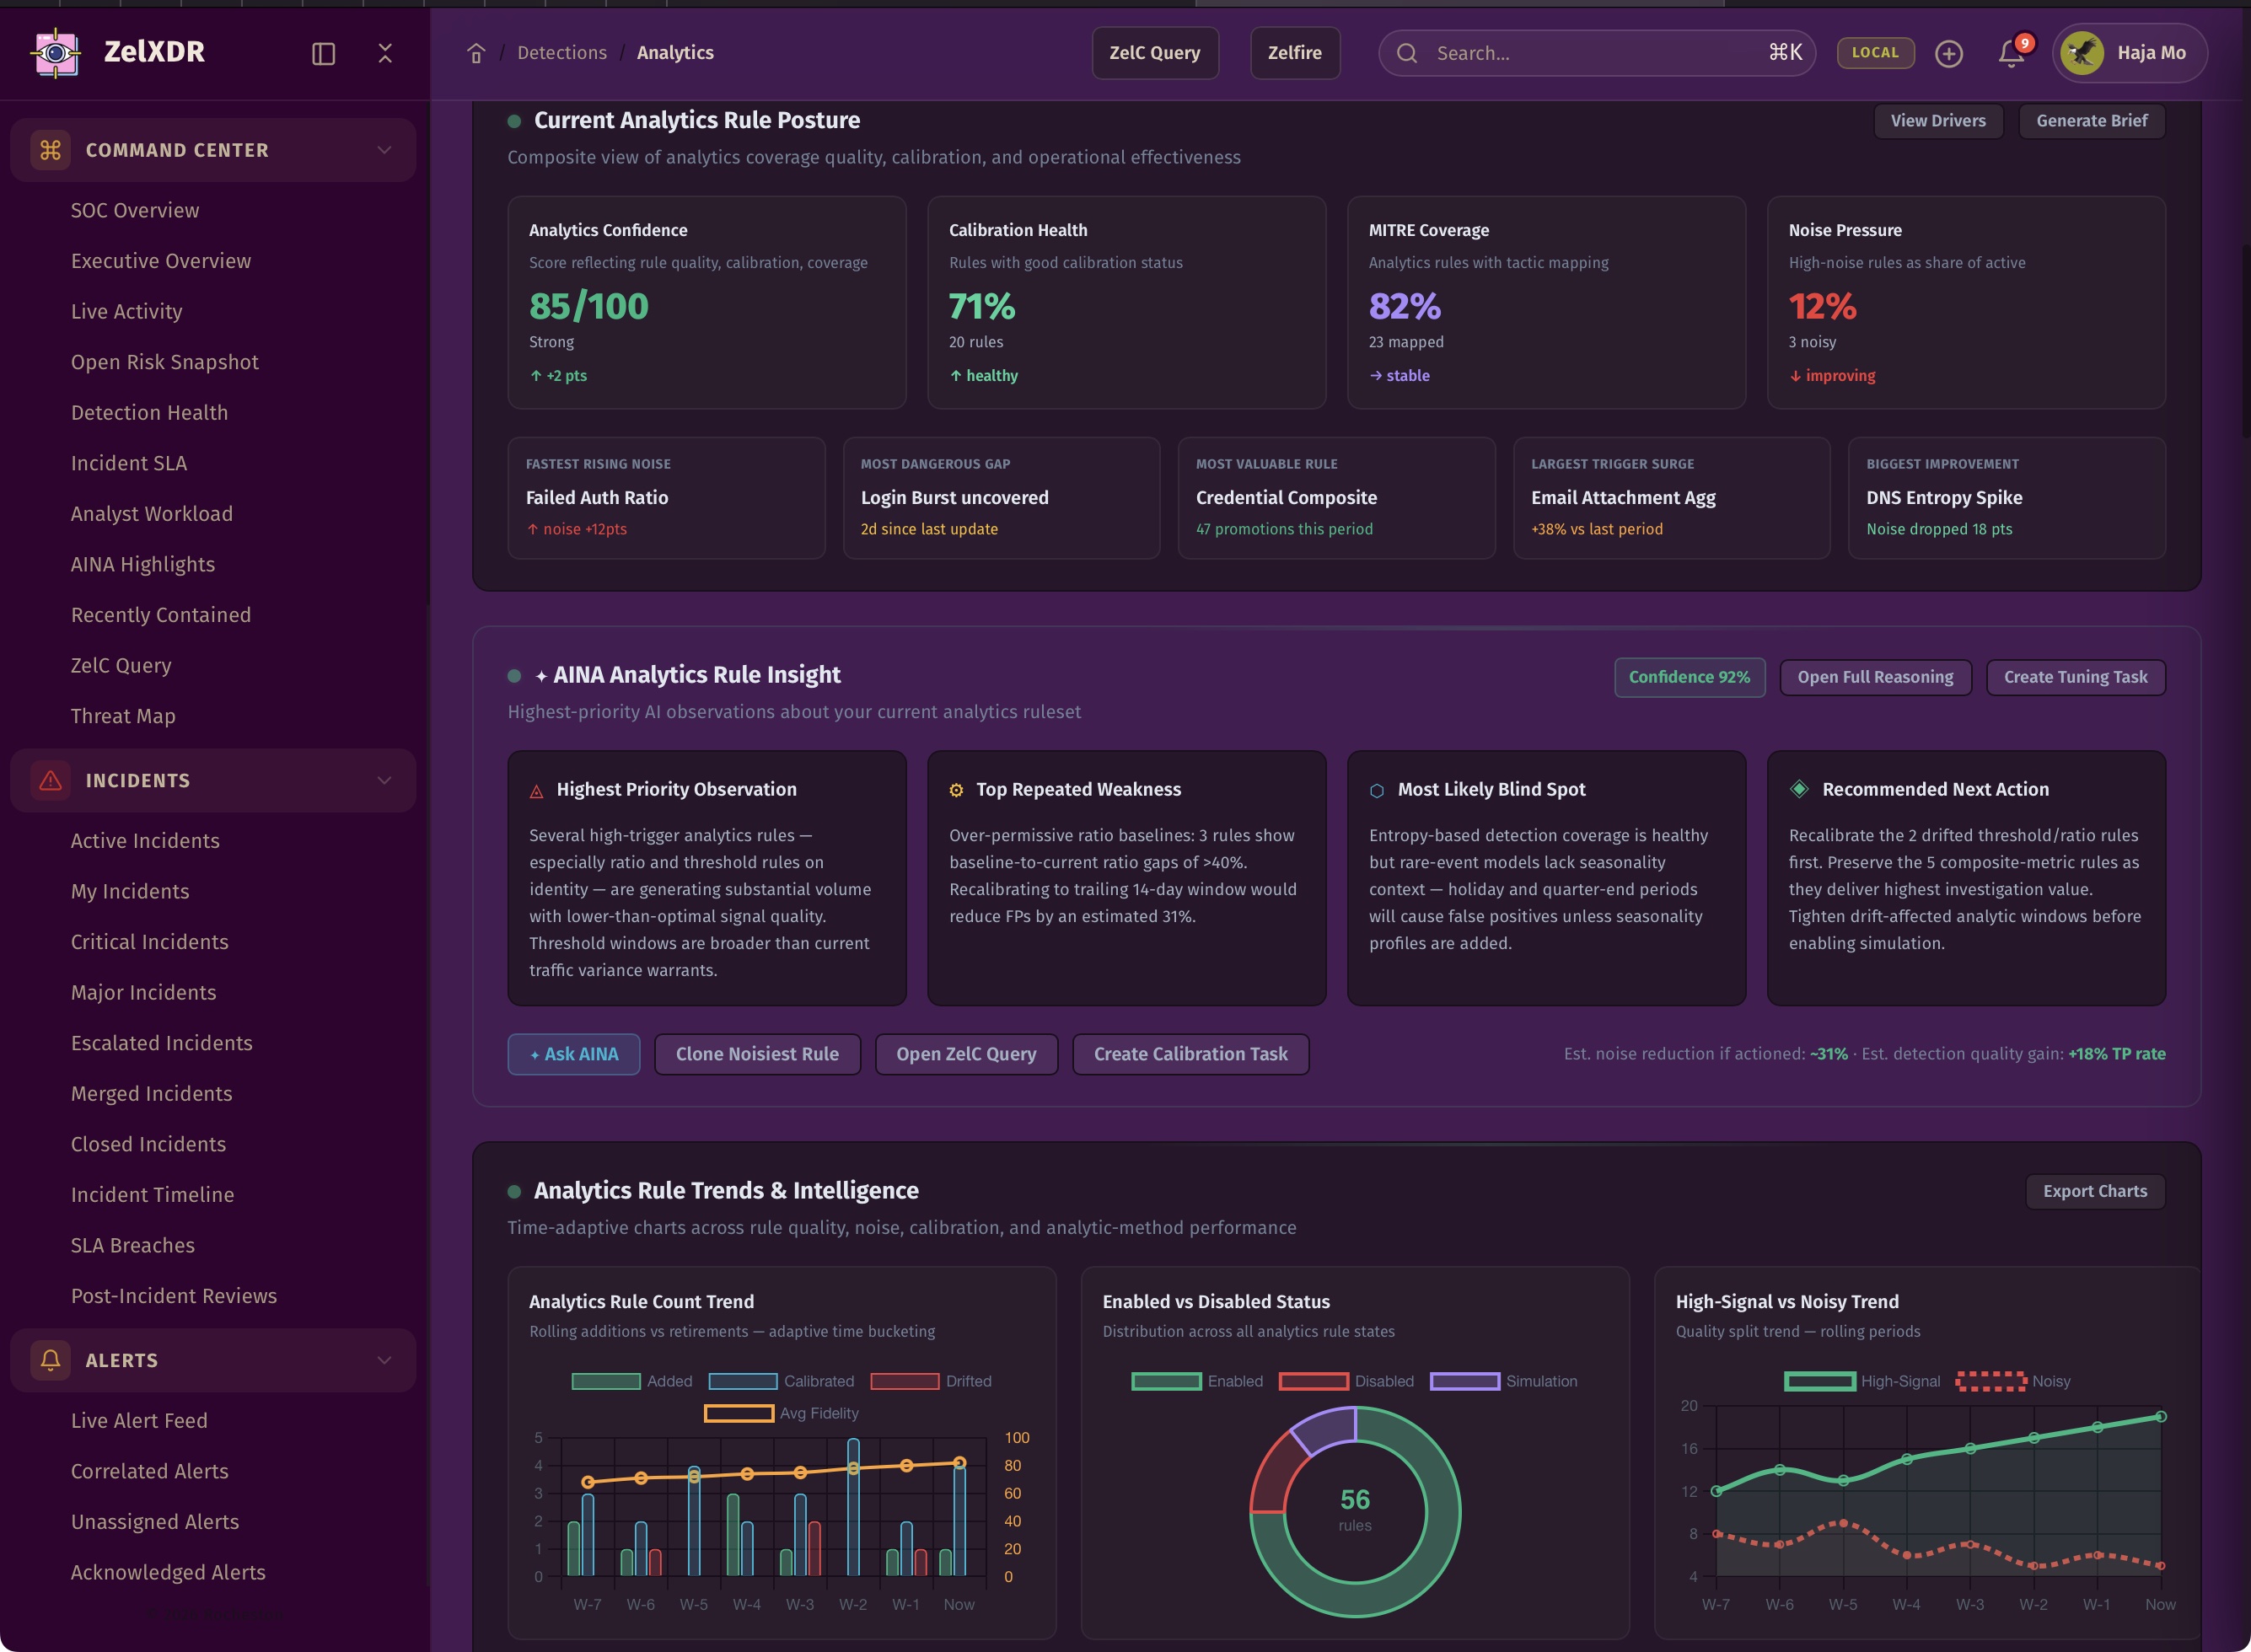
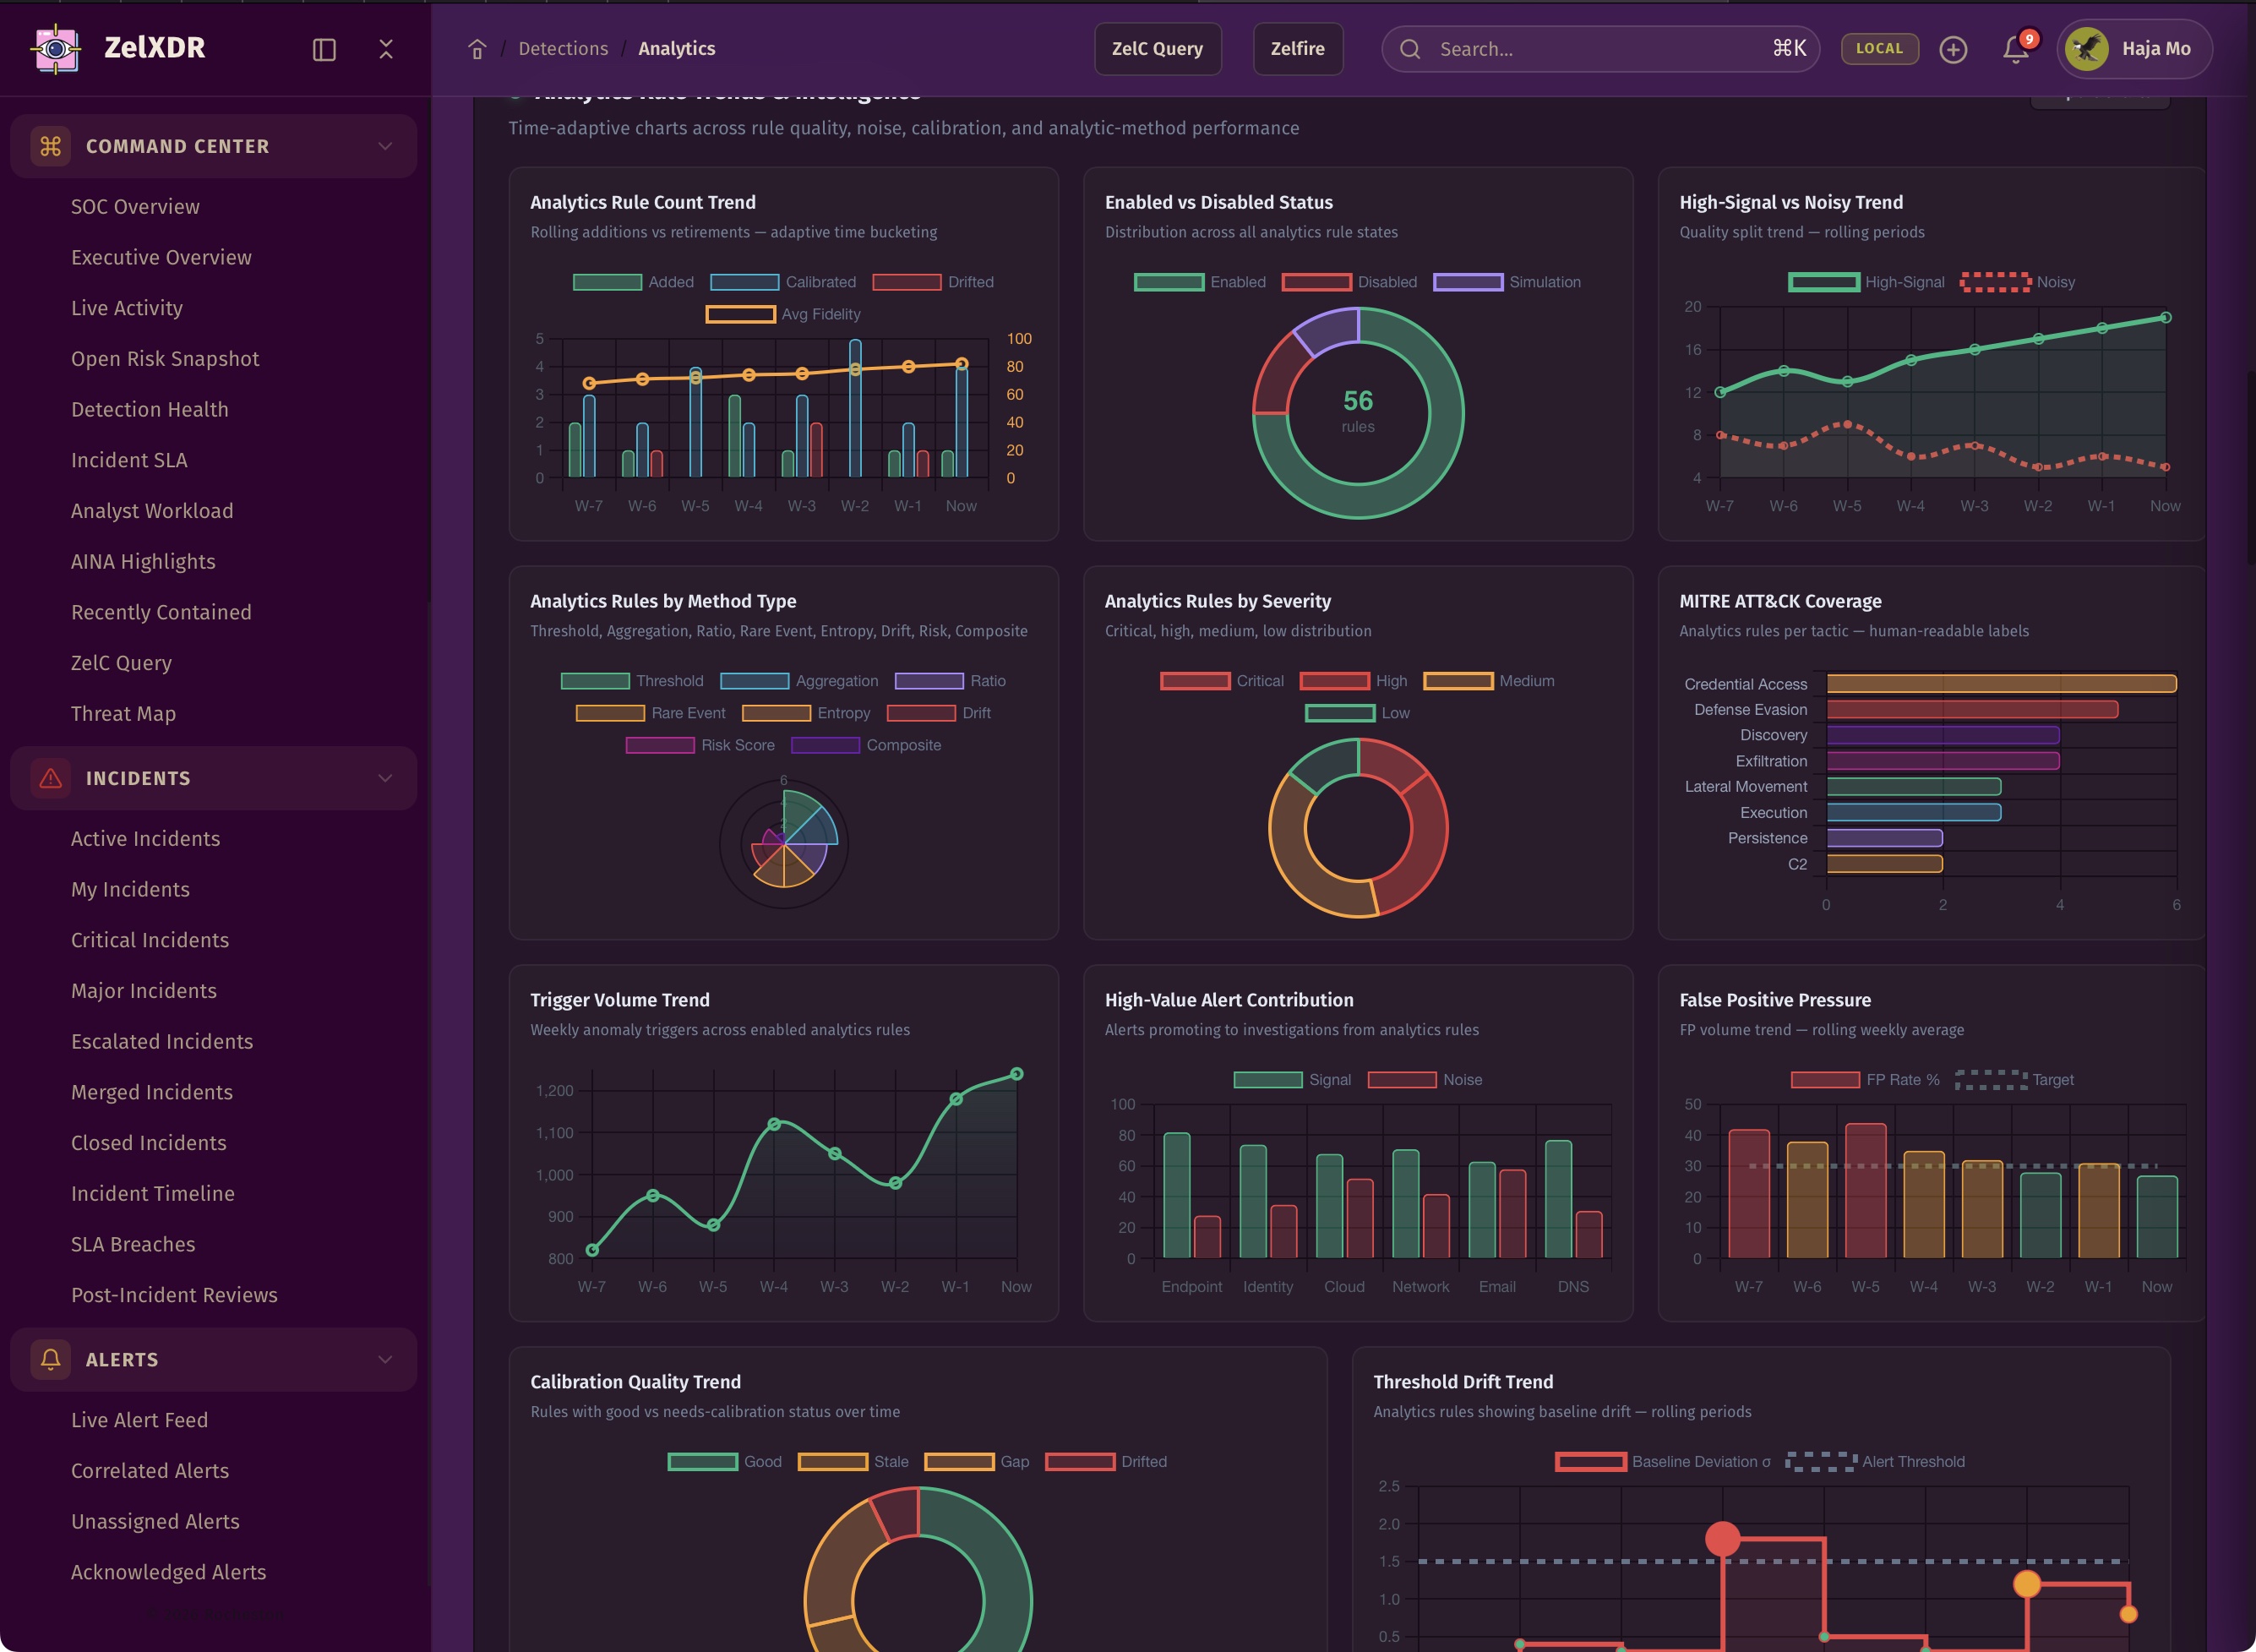
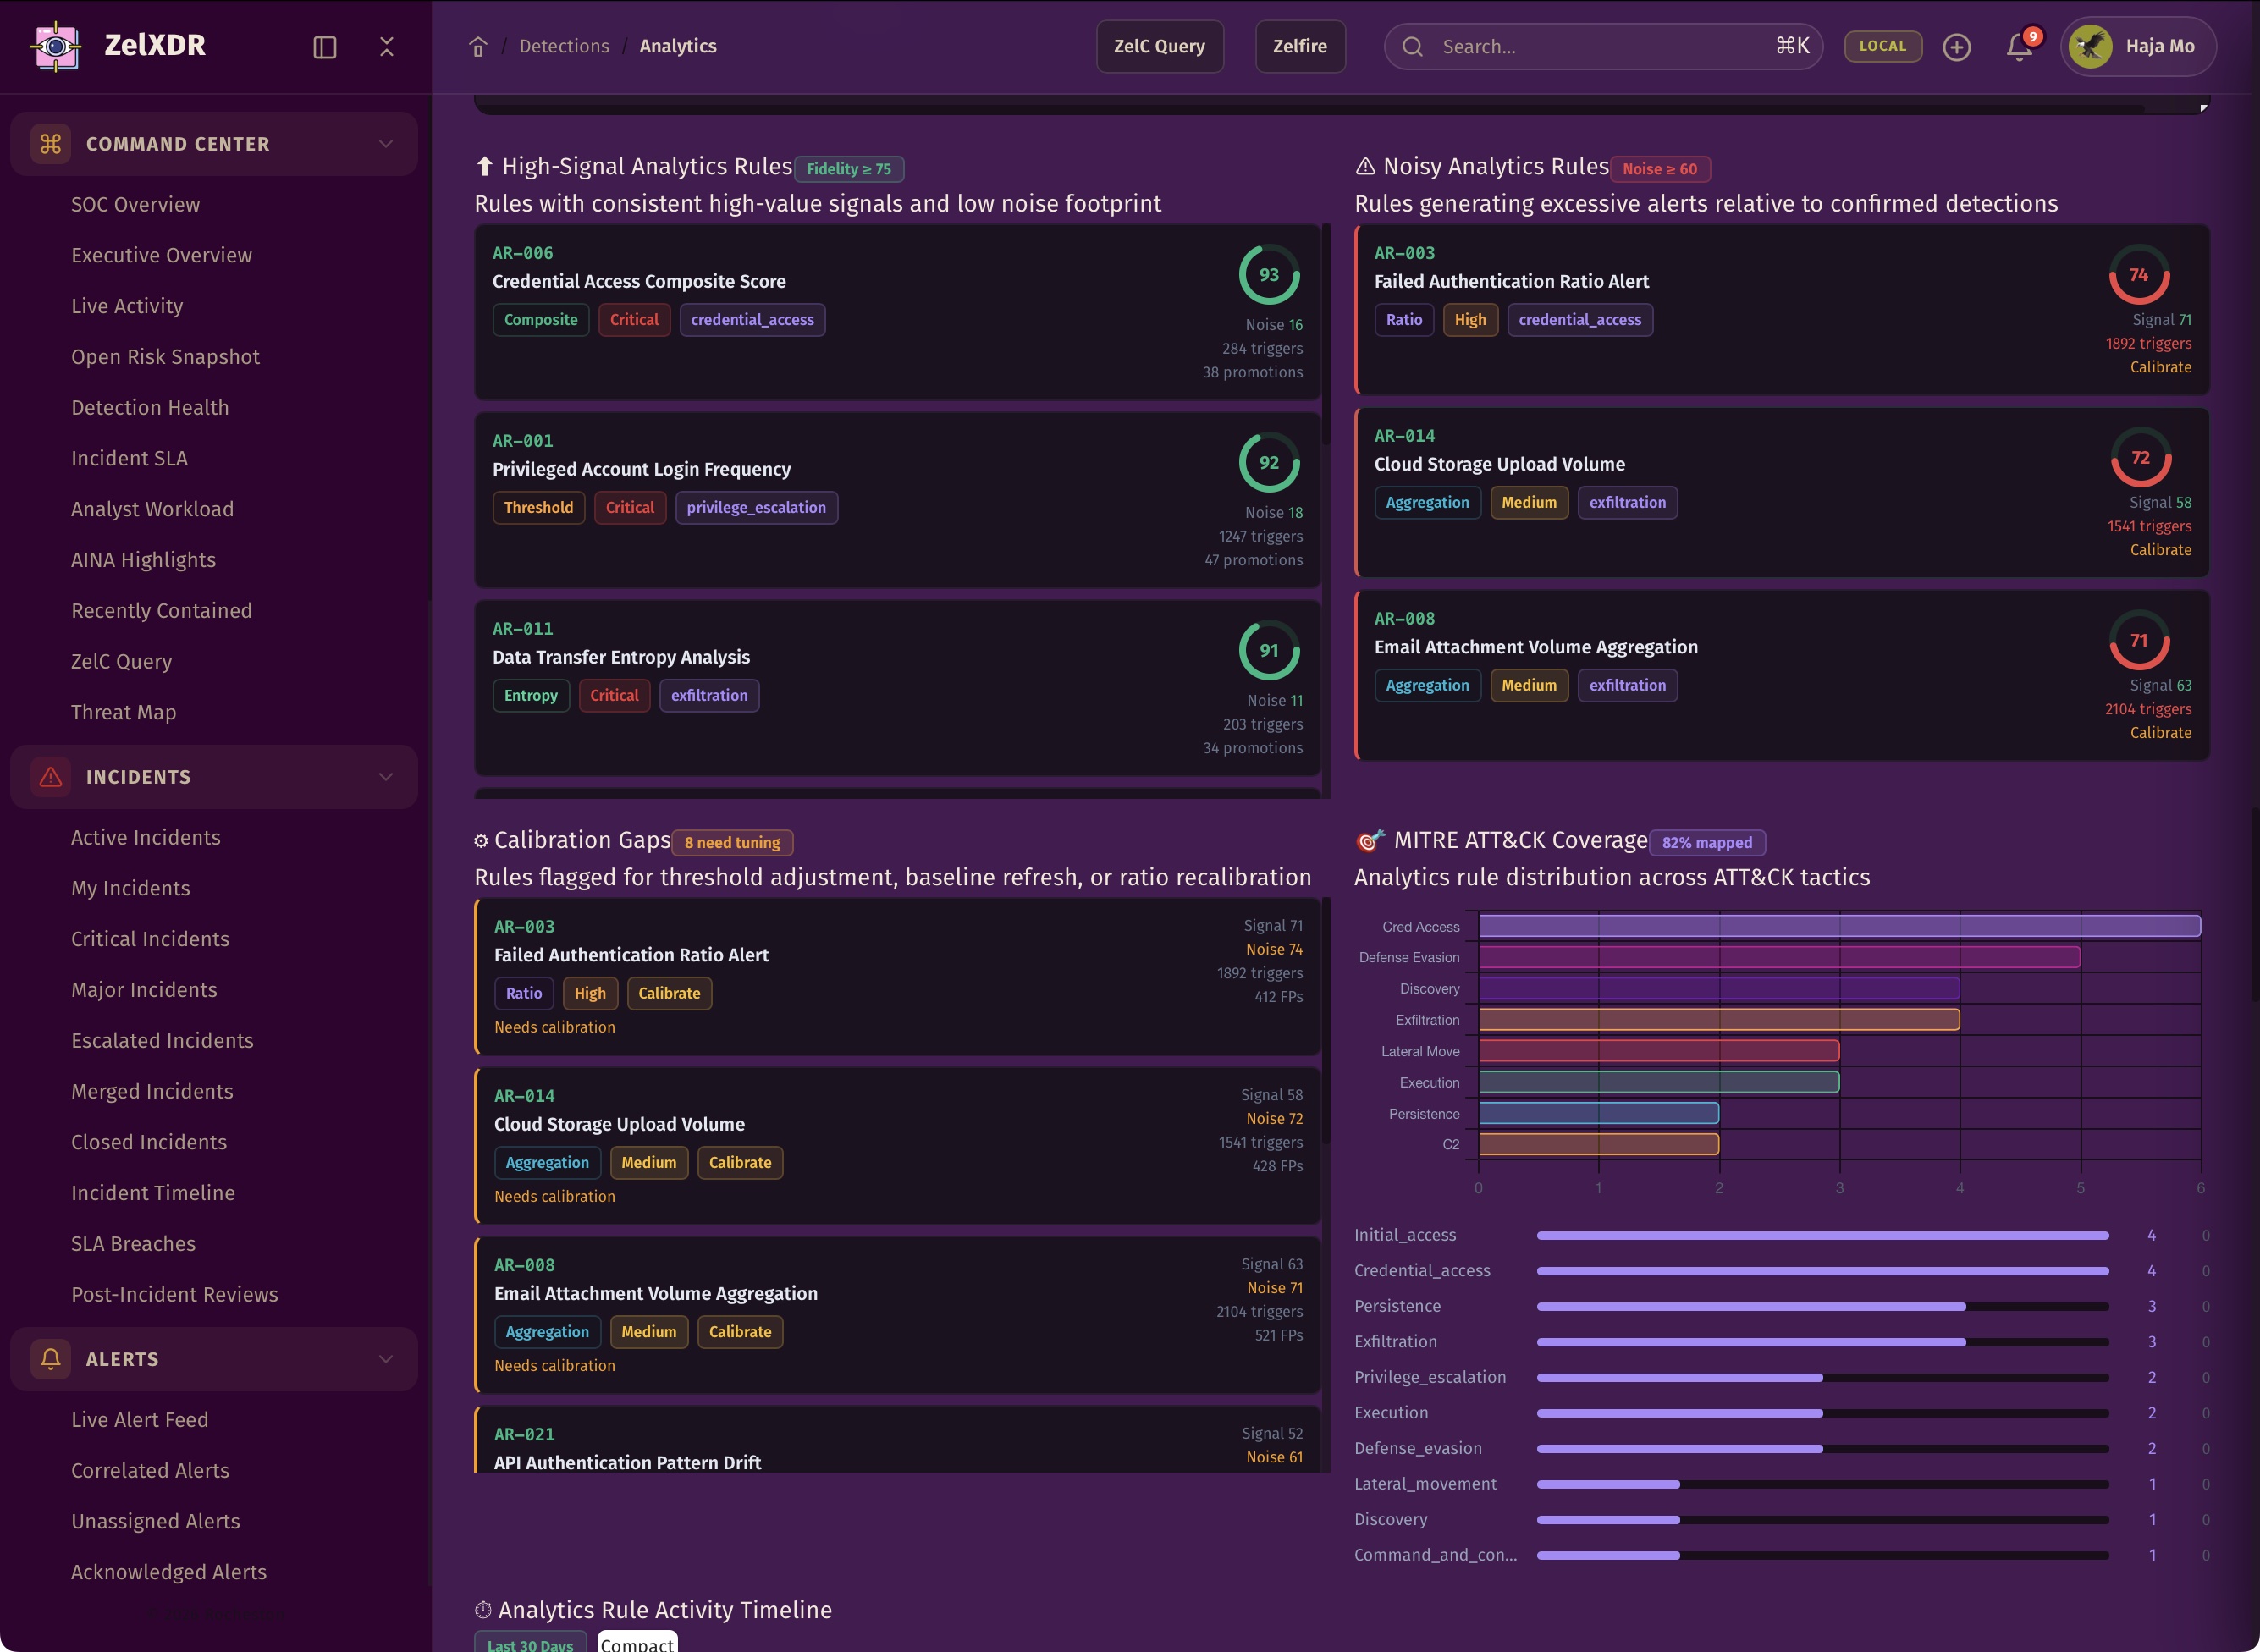
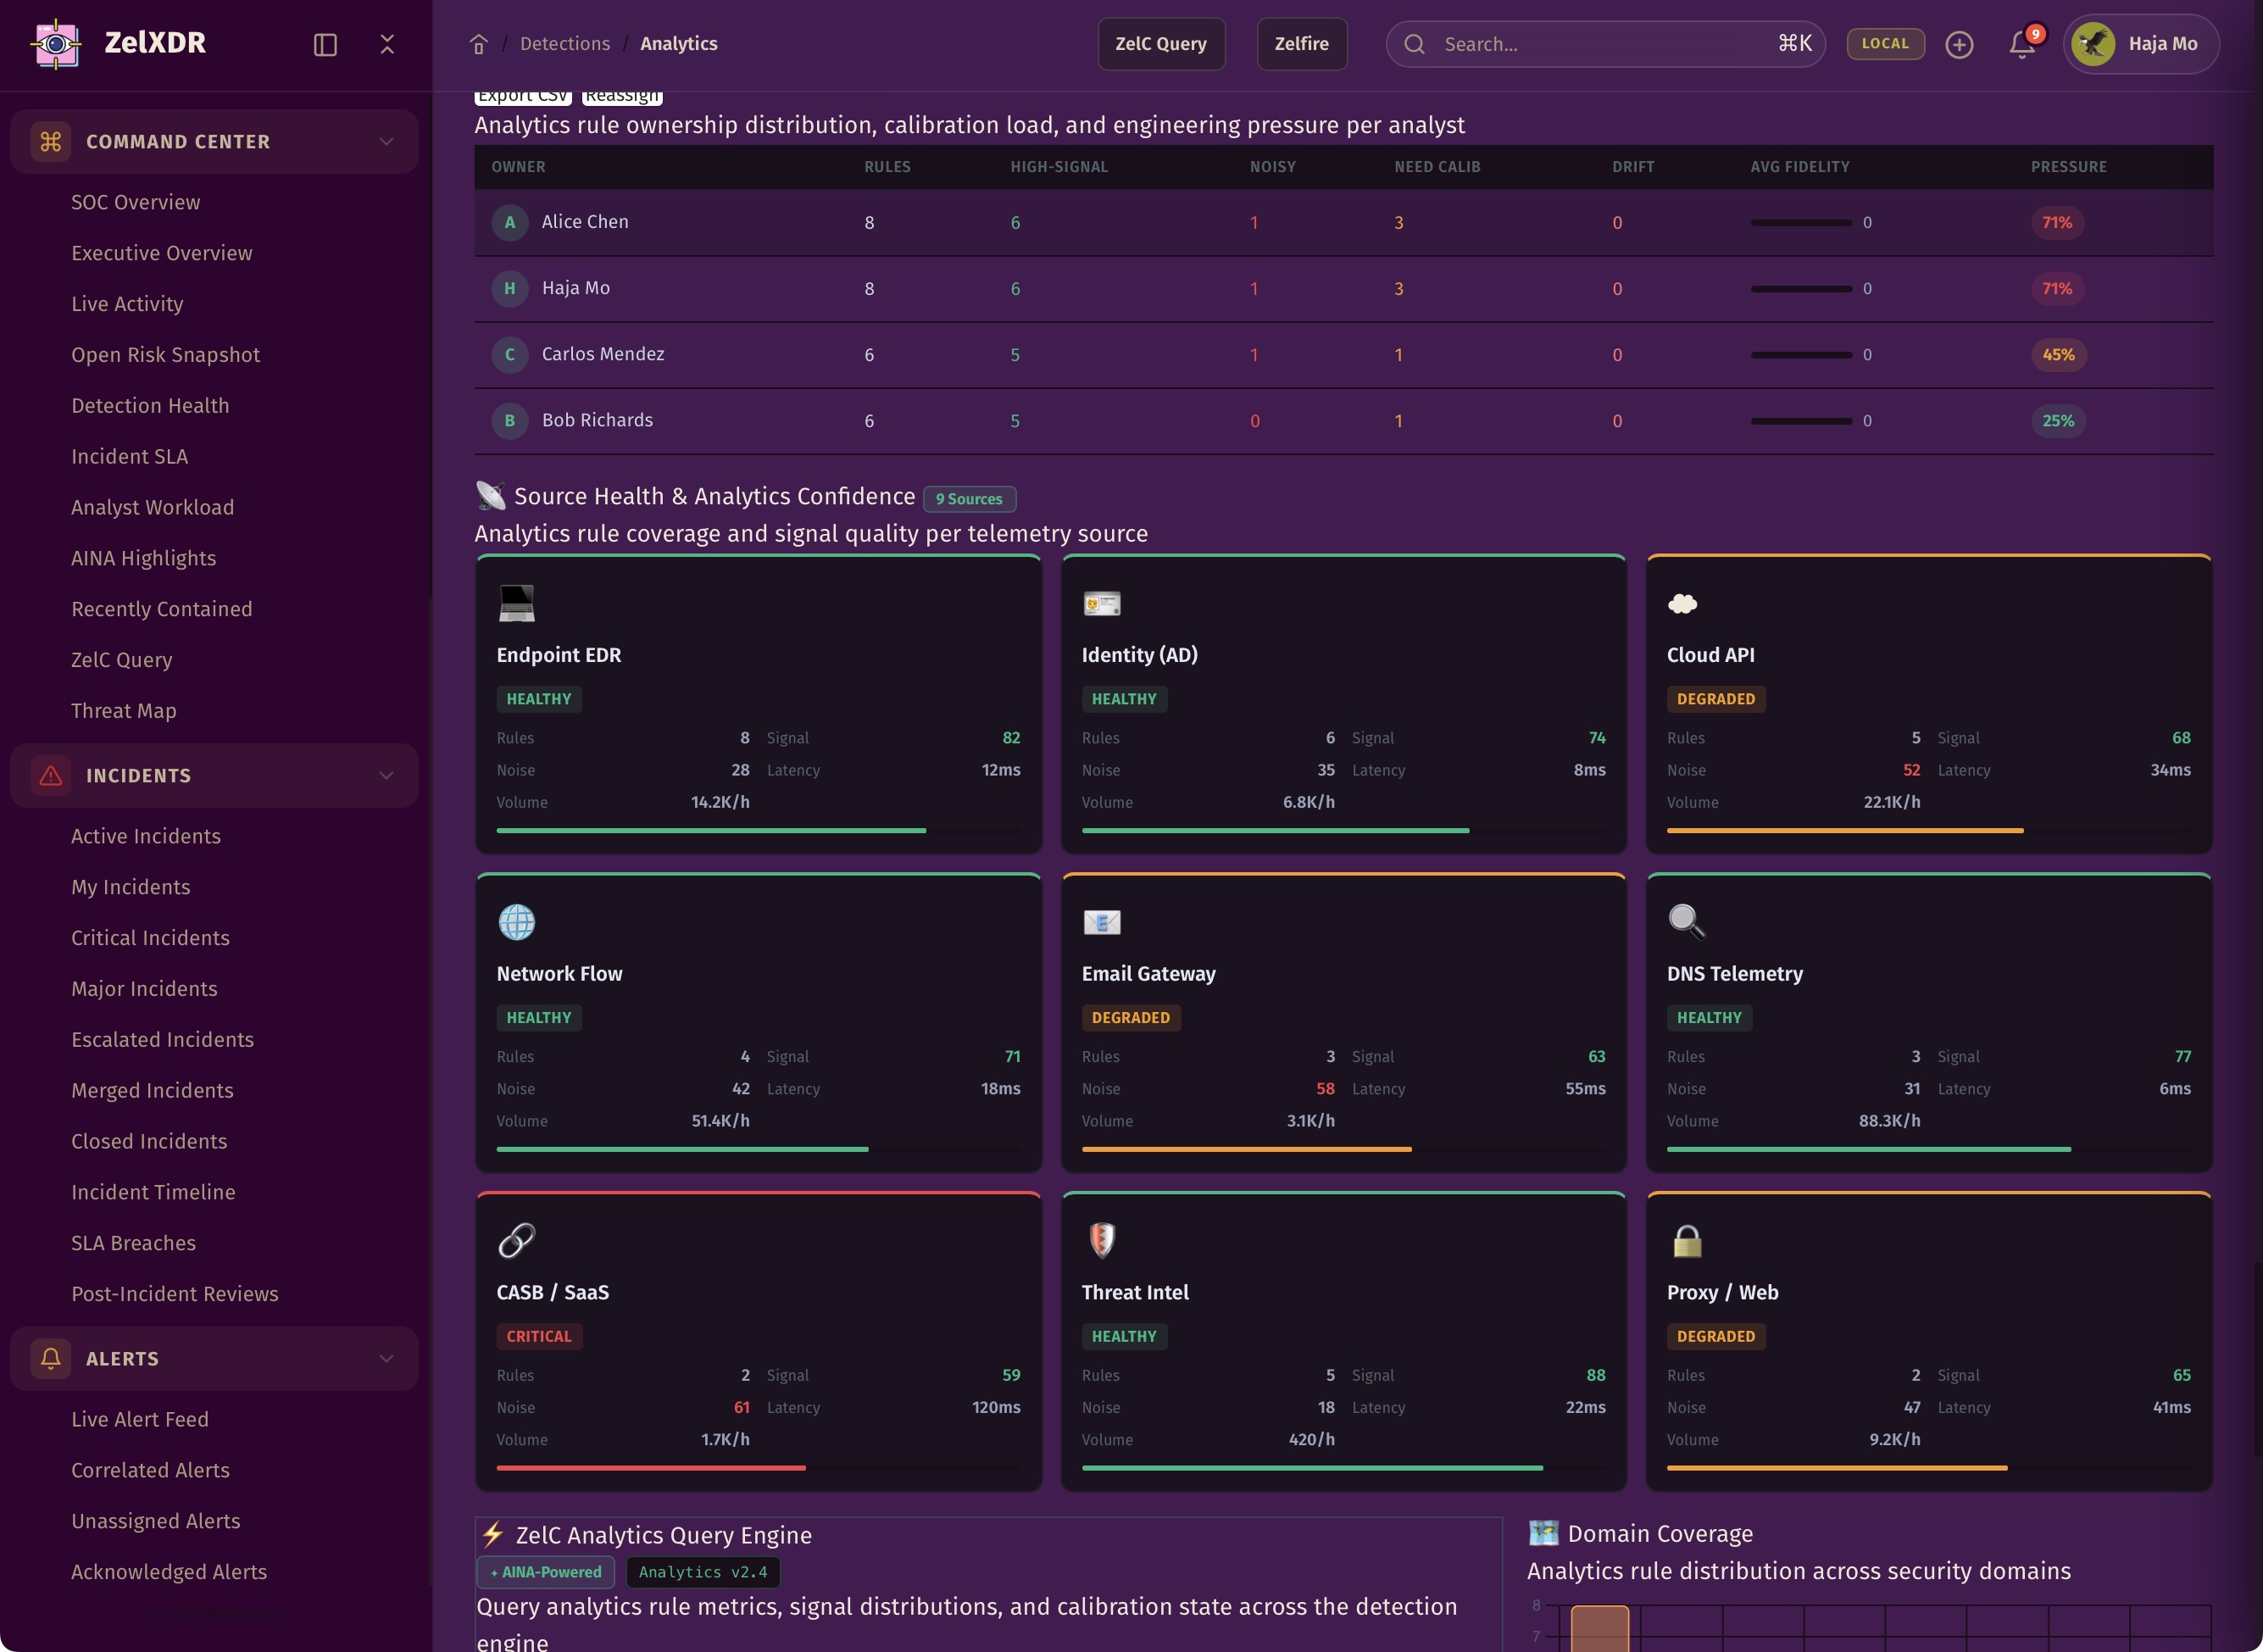
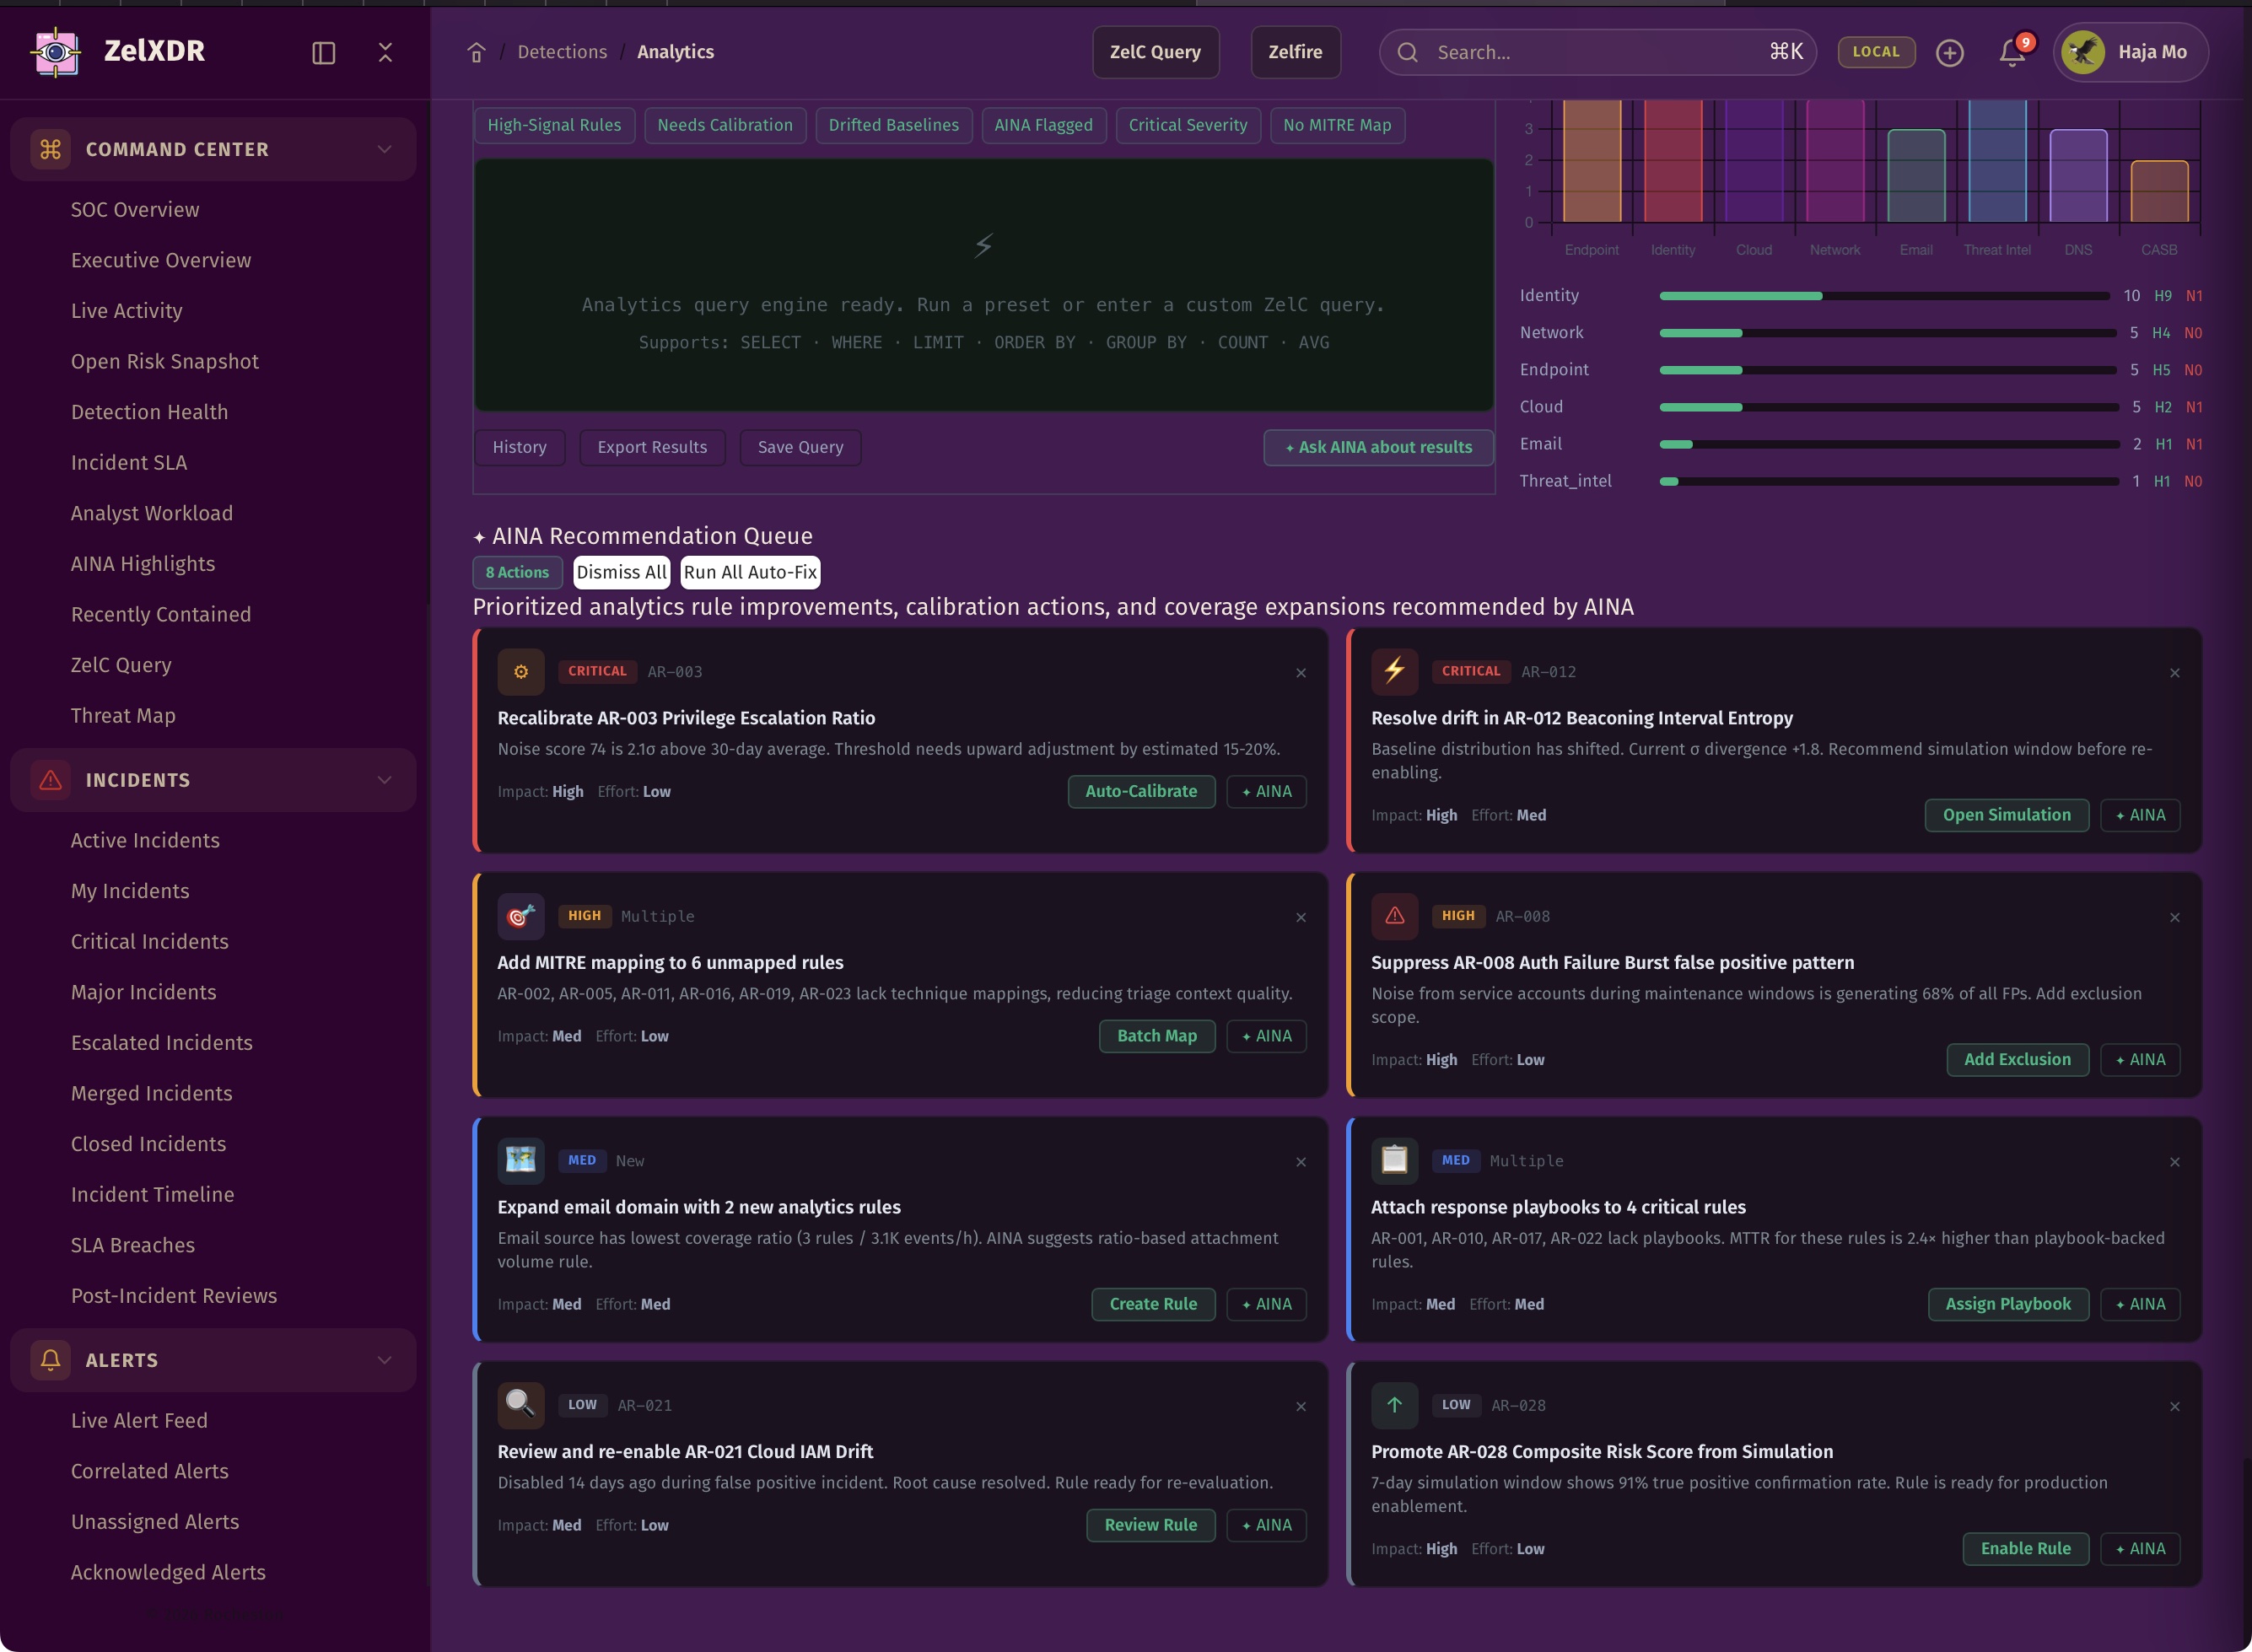
Thresholds, ratios, drift metrics, entropy, rare-event models, and composite scoring all come together in ZelXDR to create richer security analytics that go beyond basic matching.
Real analytics separate signal from repetition.
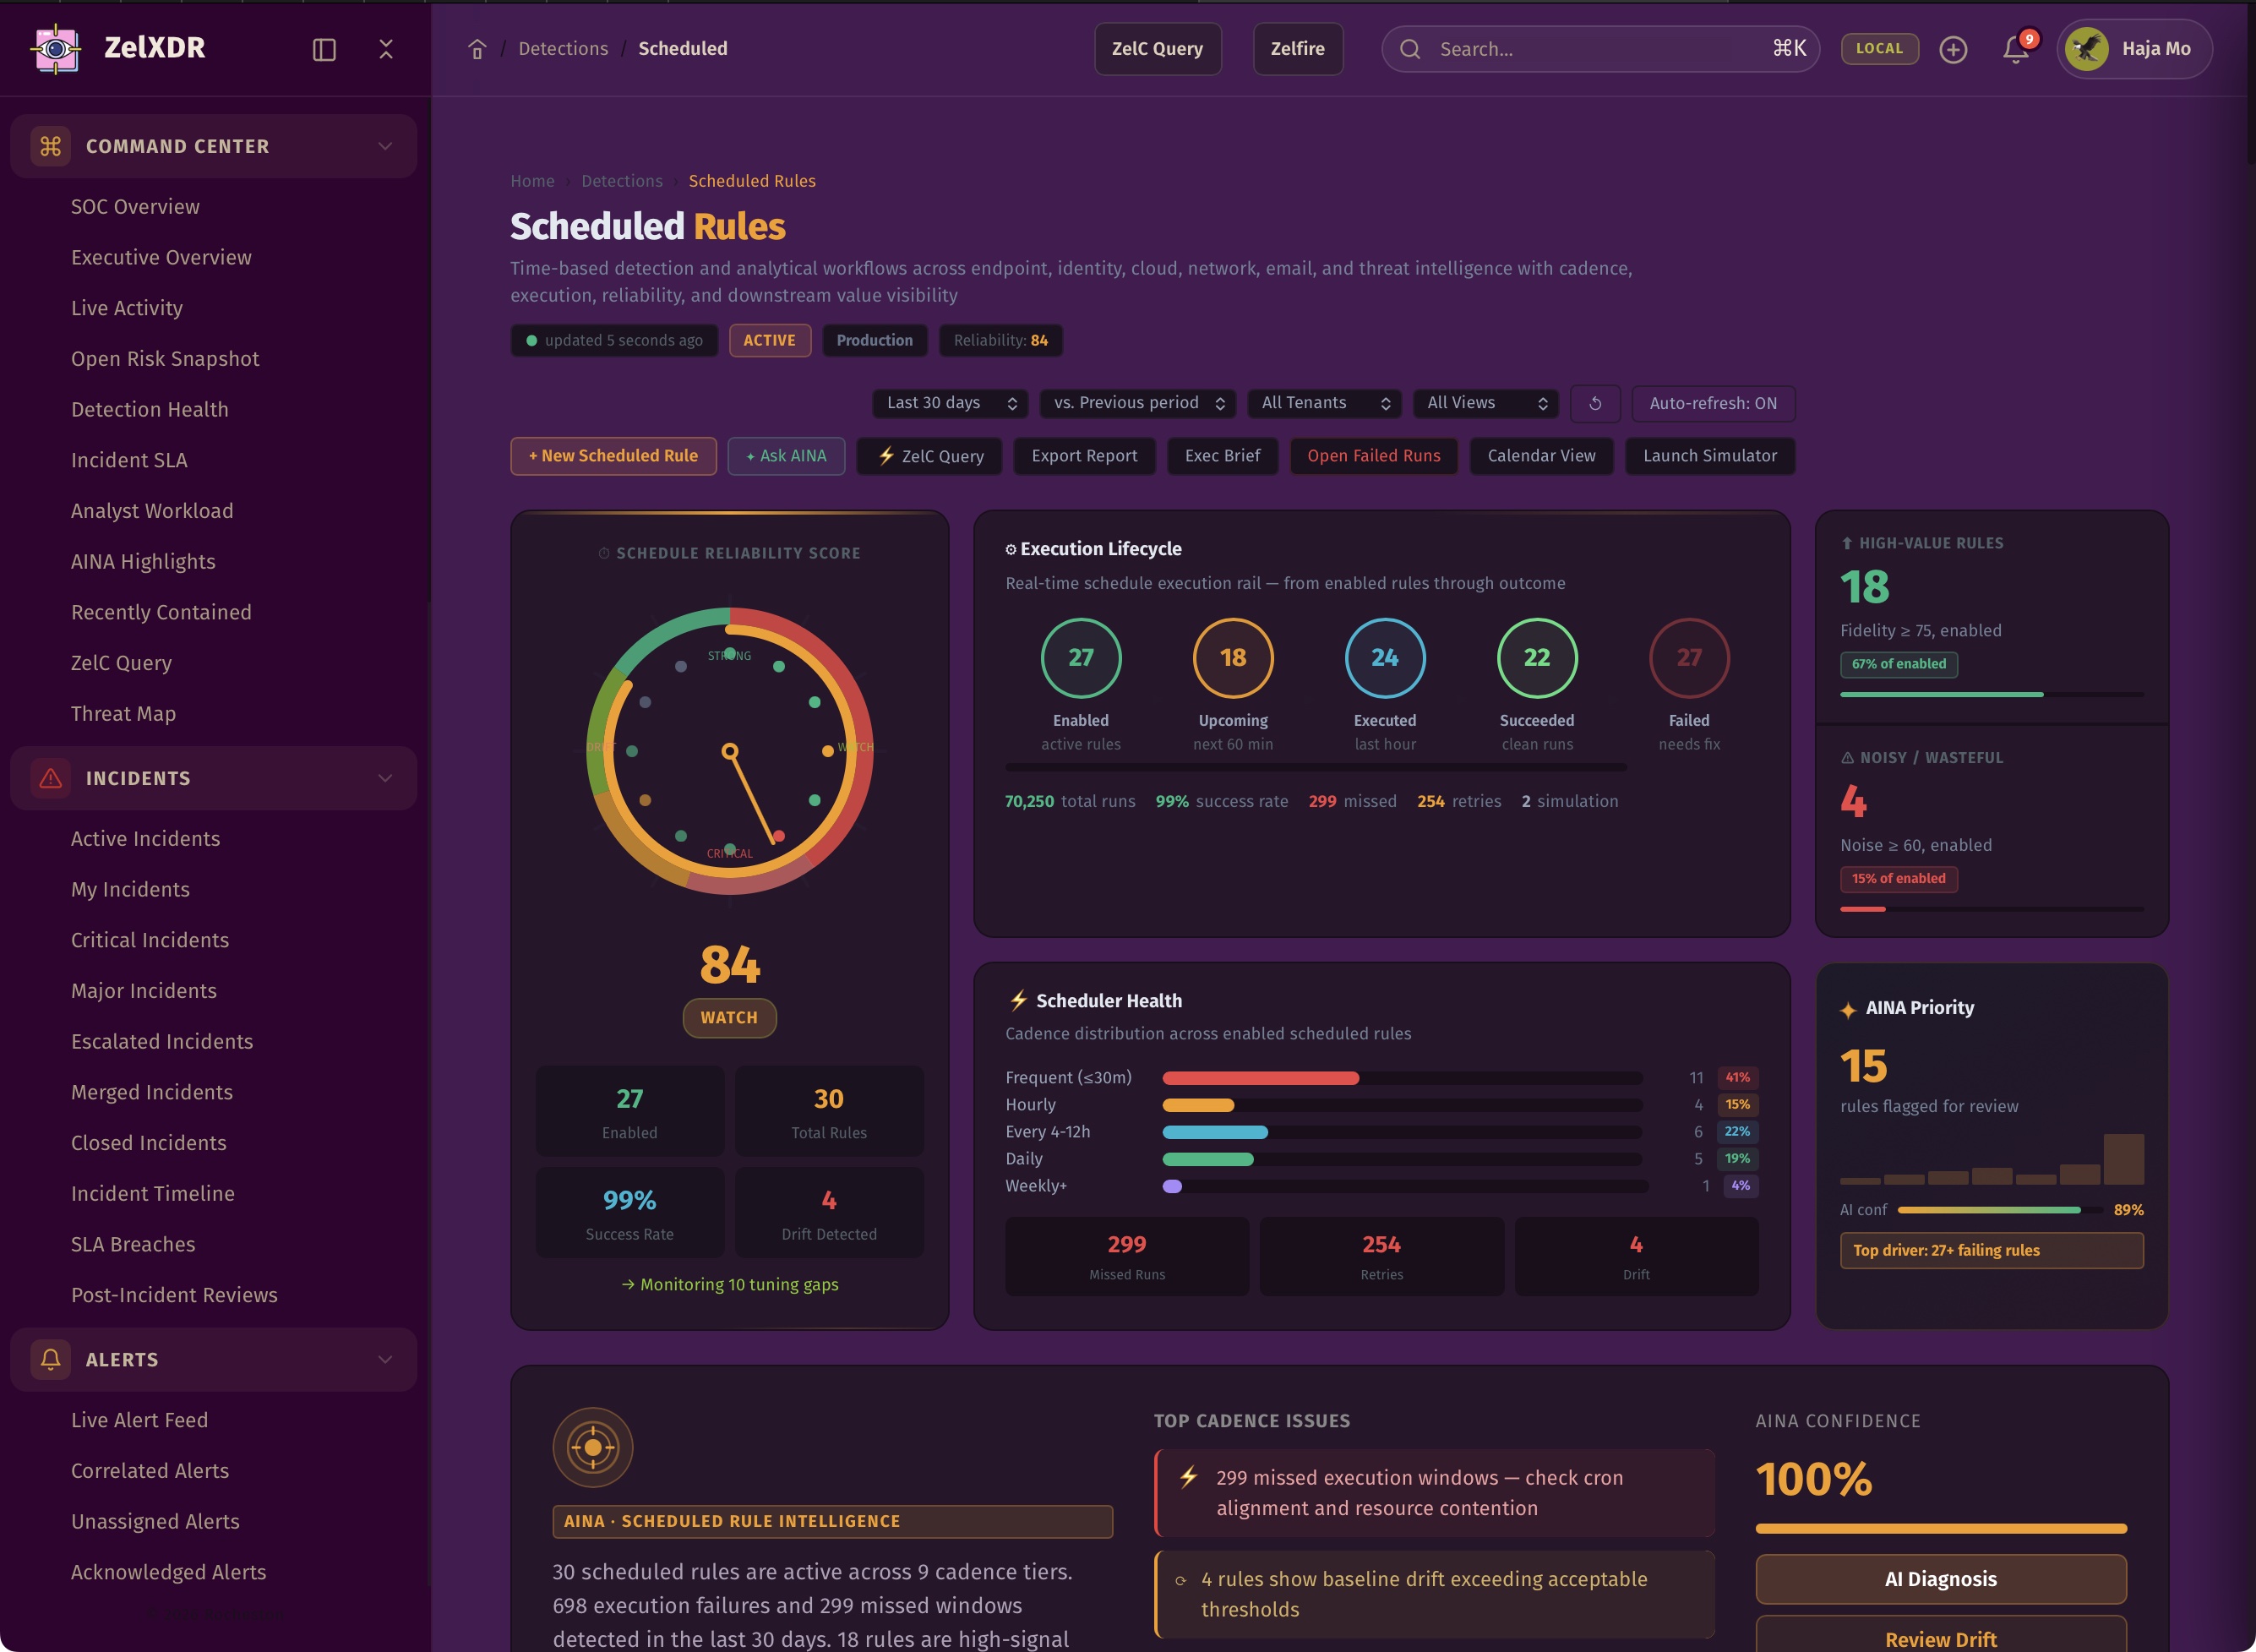
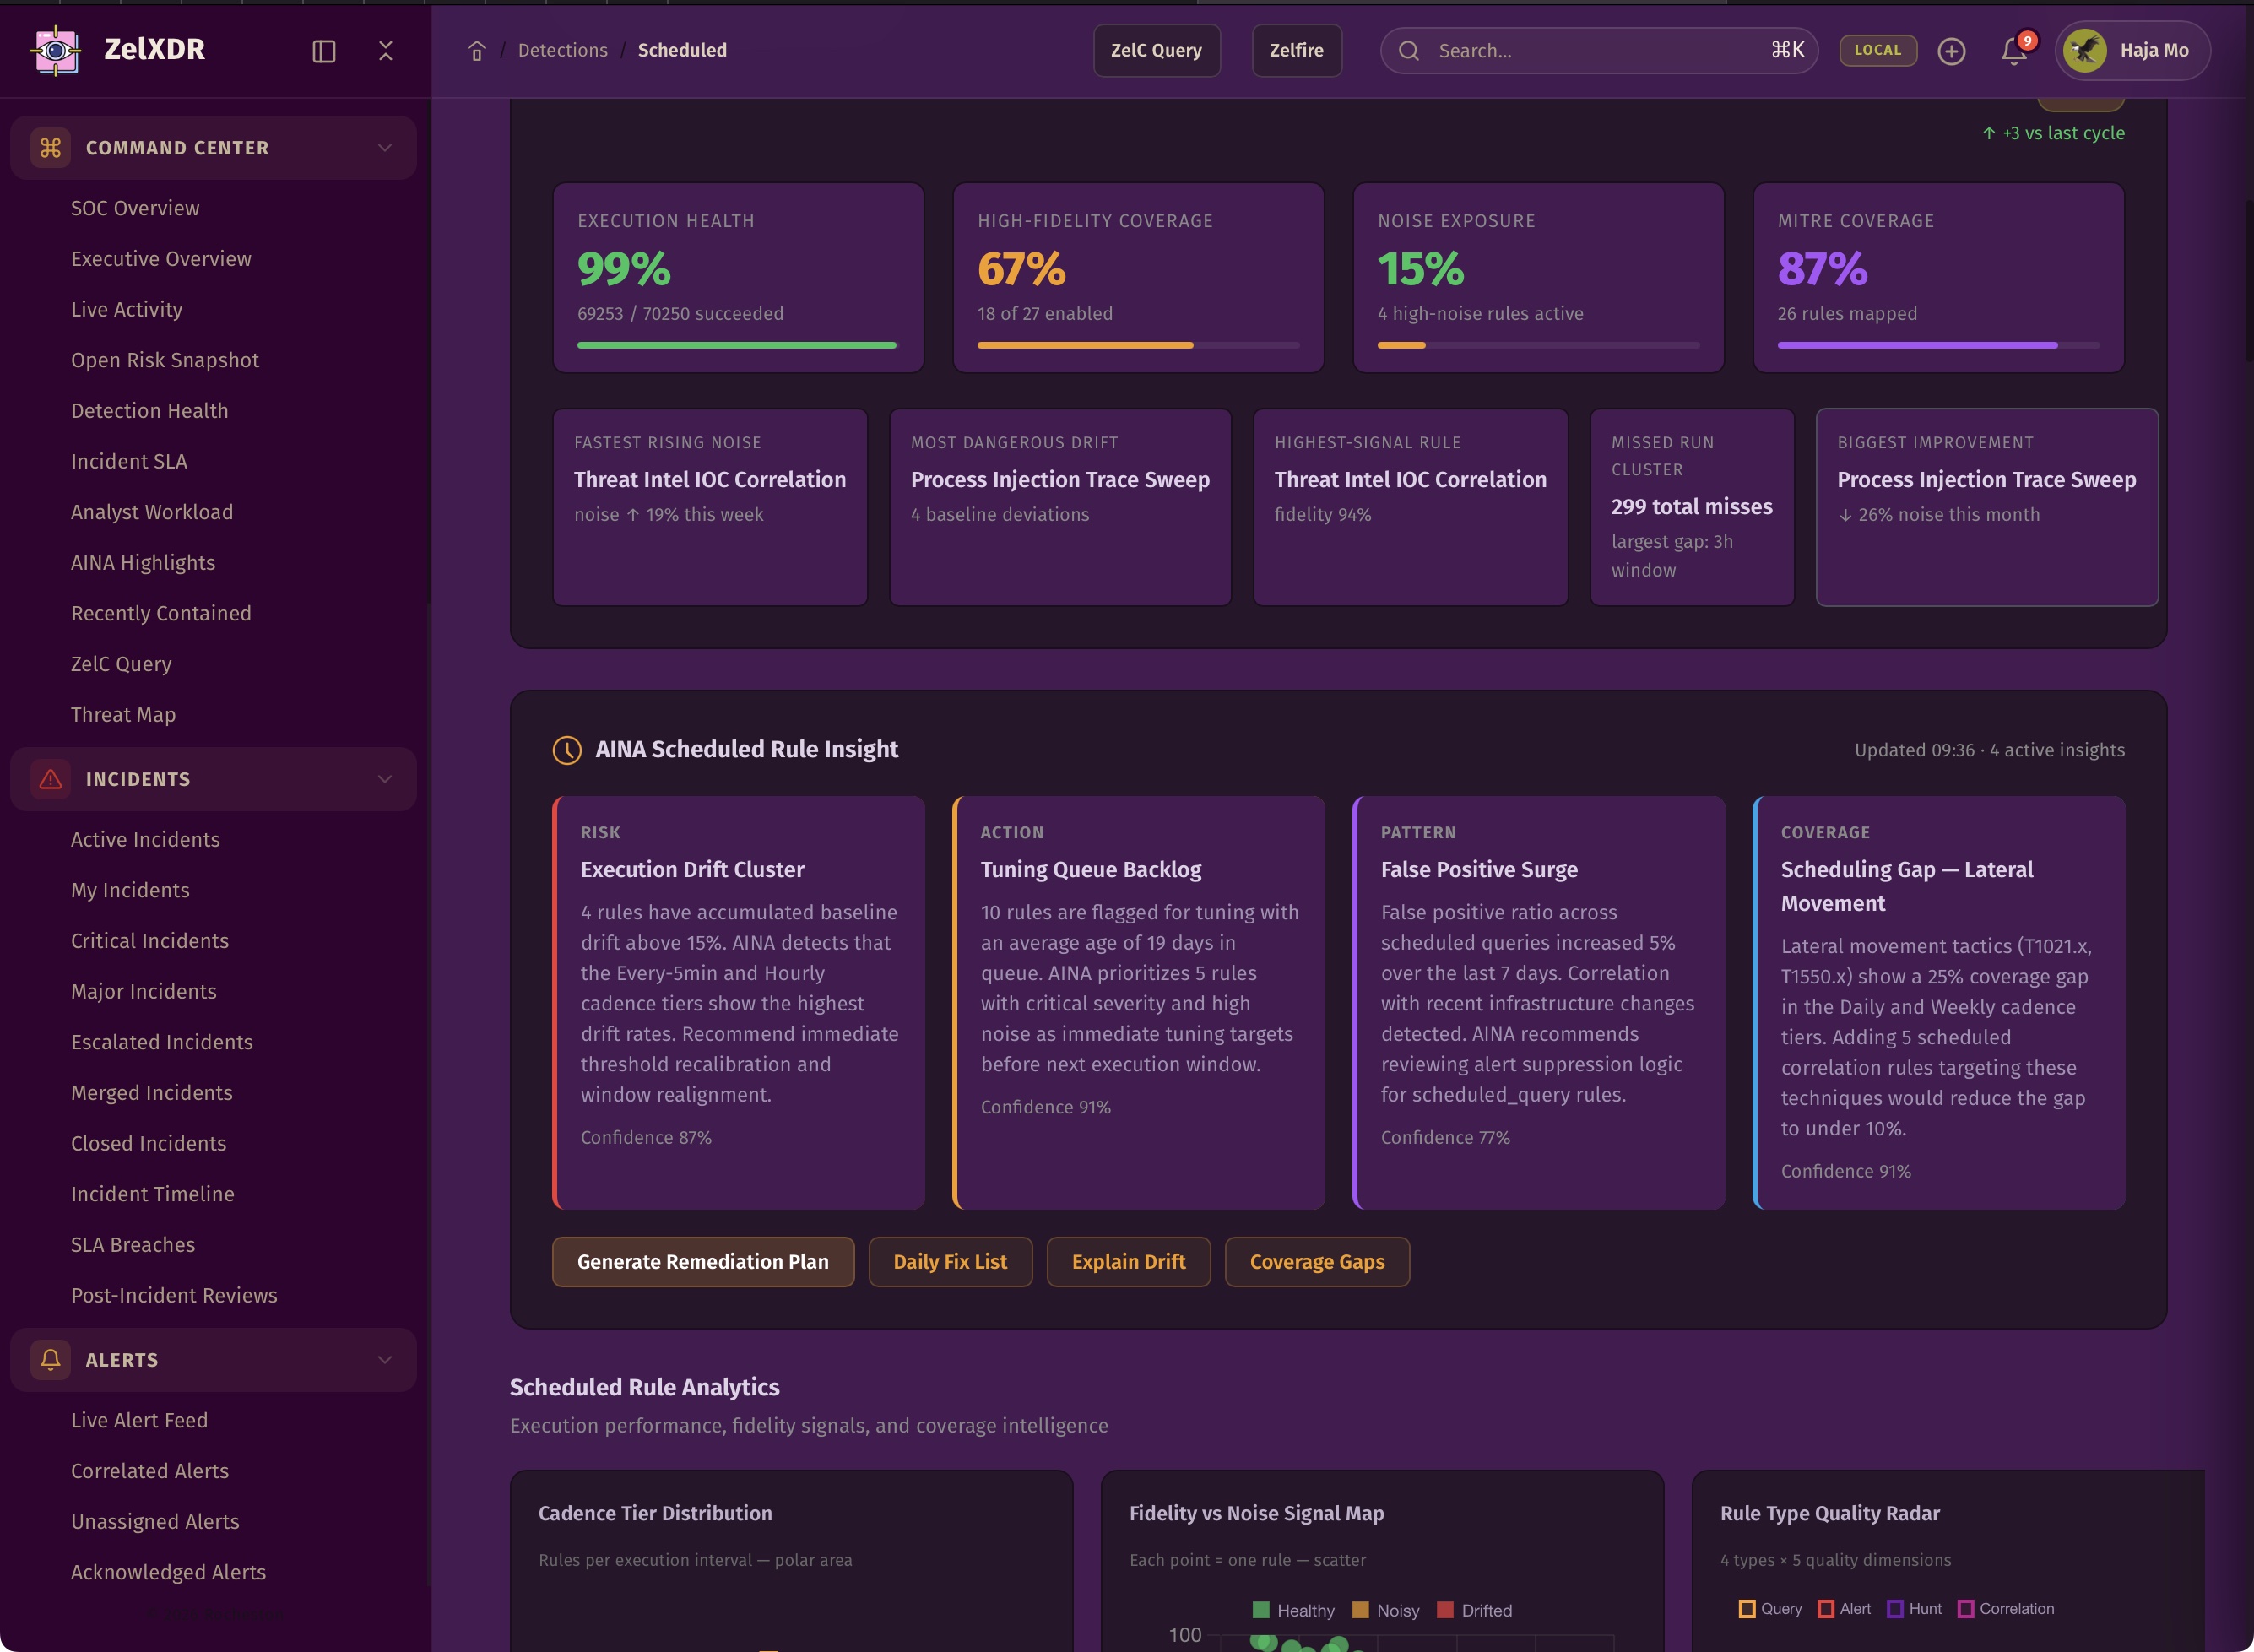
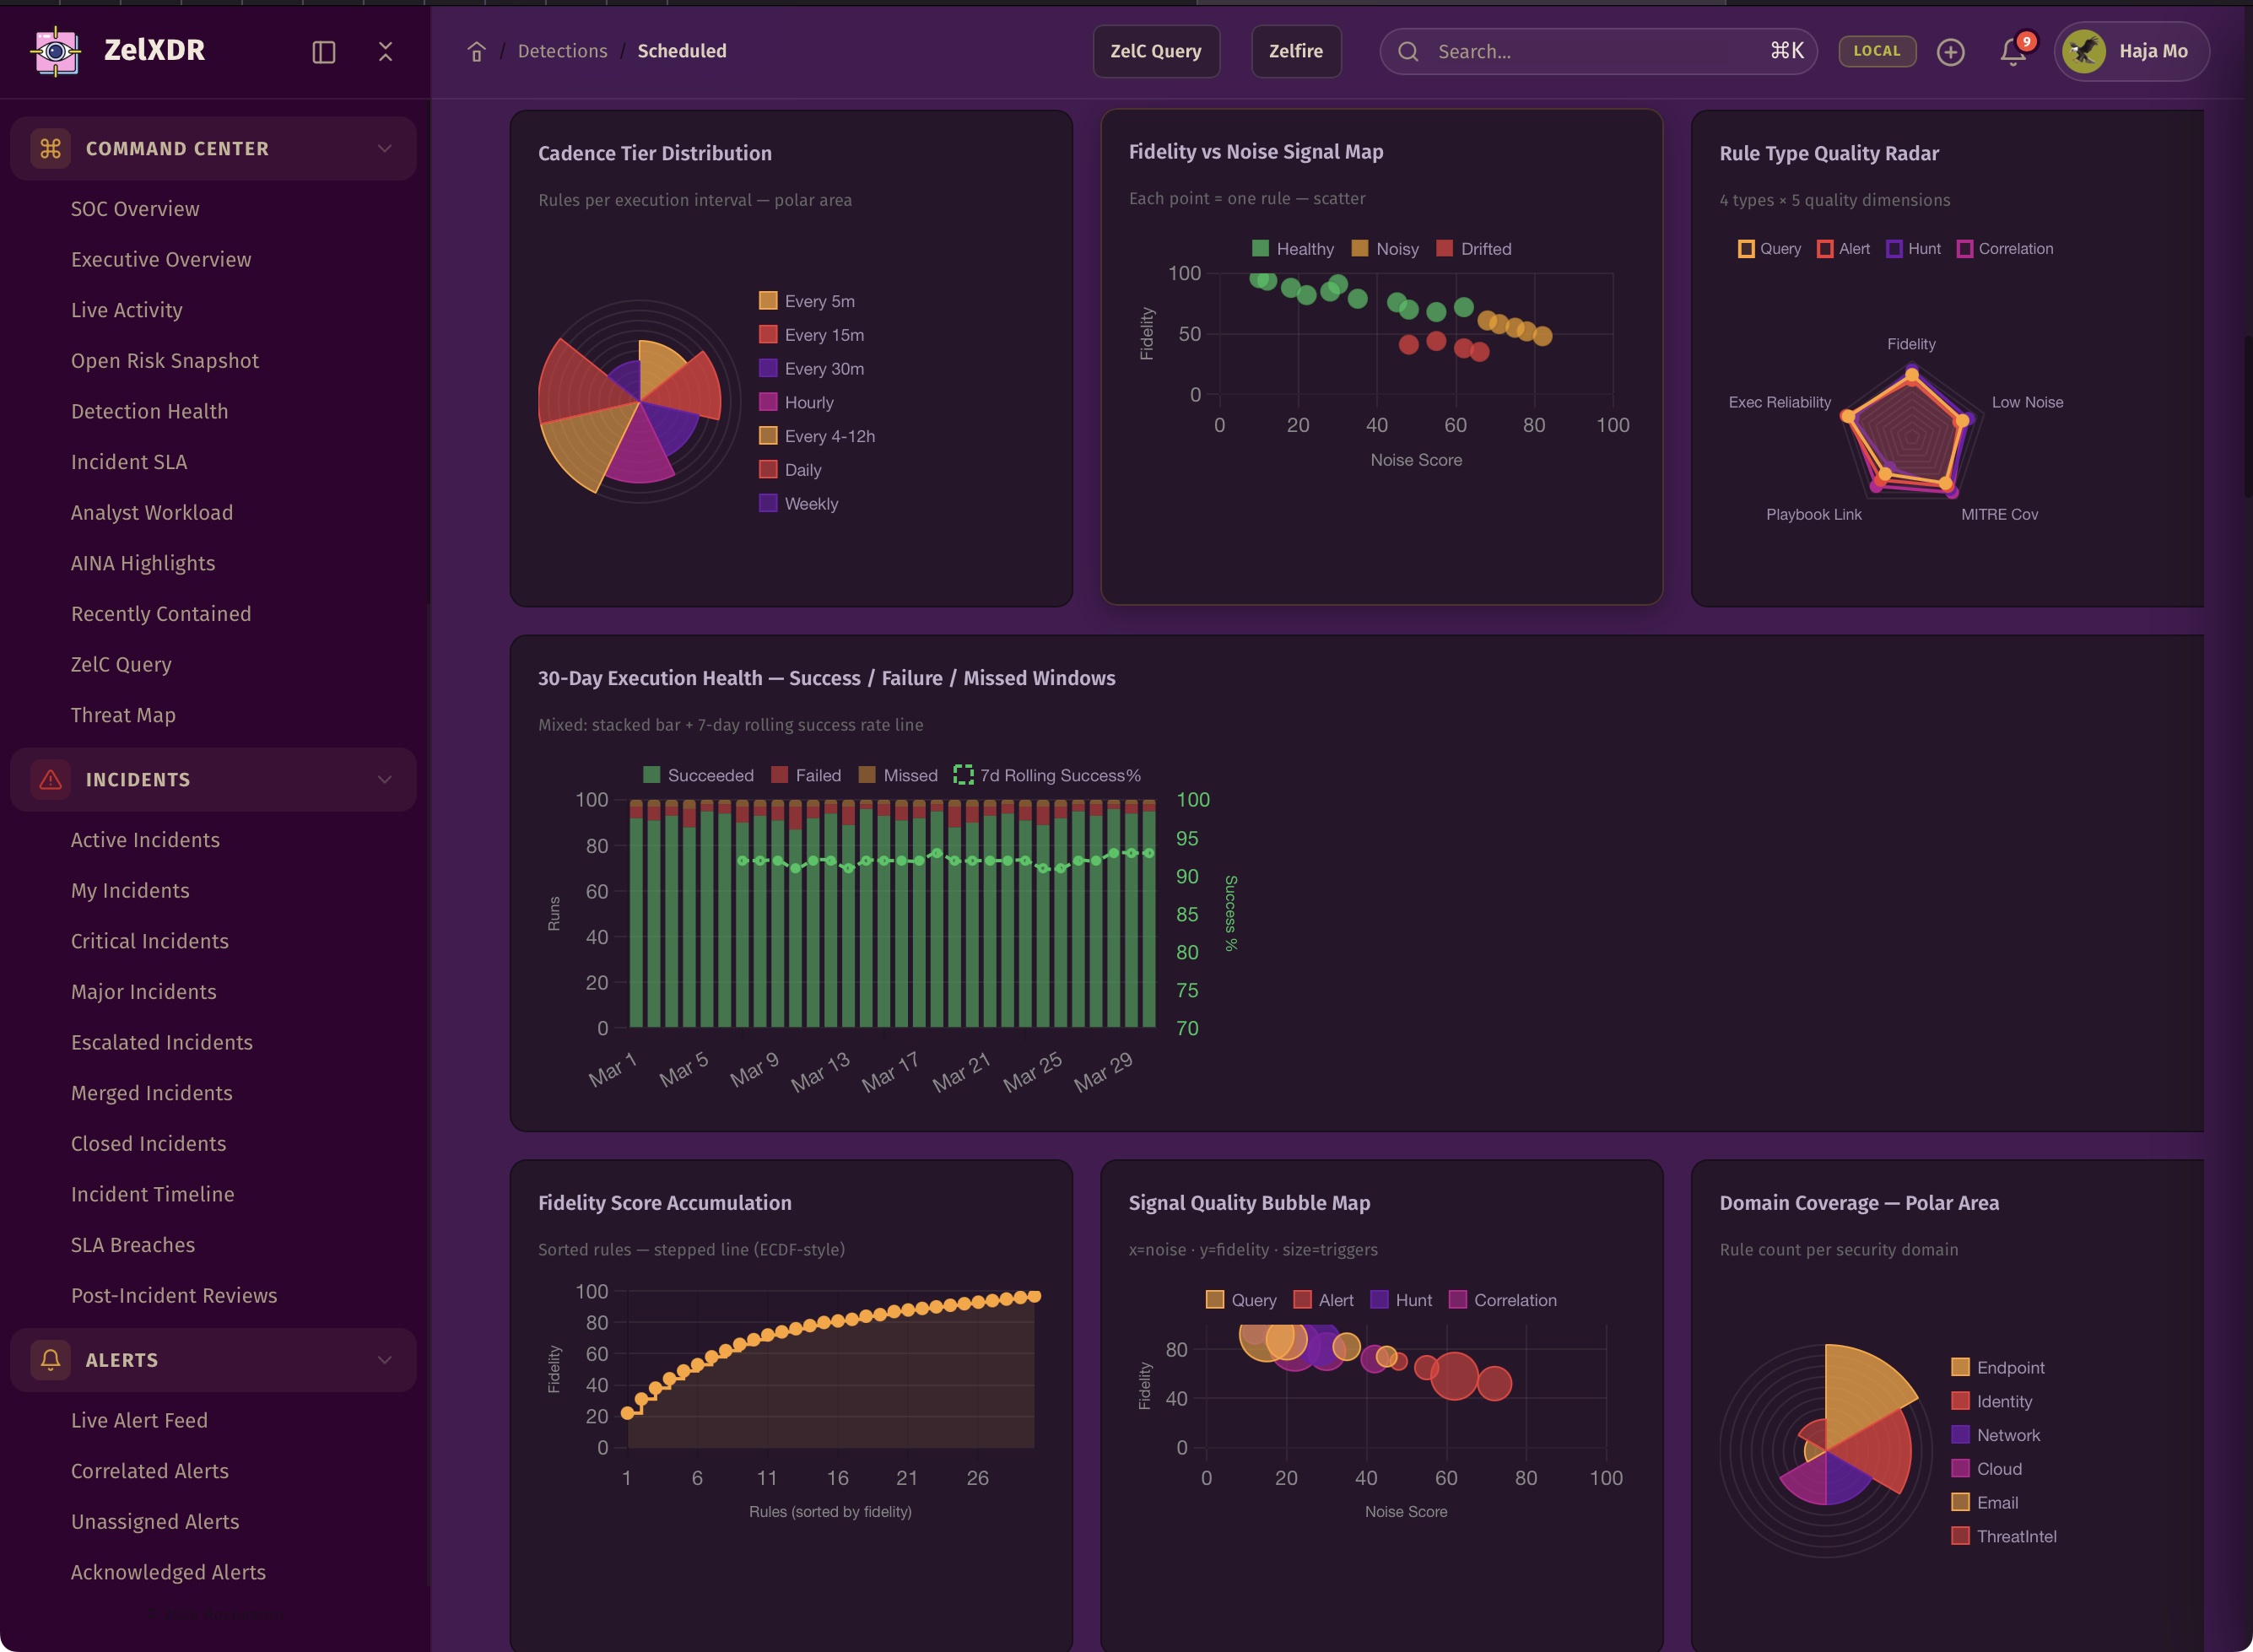
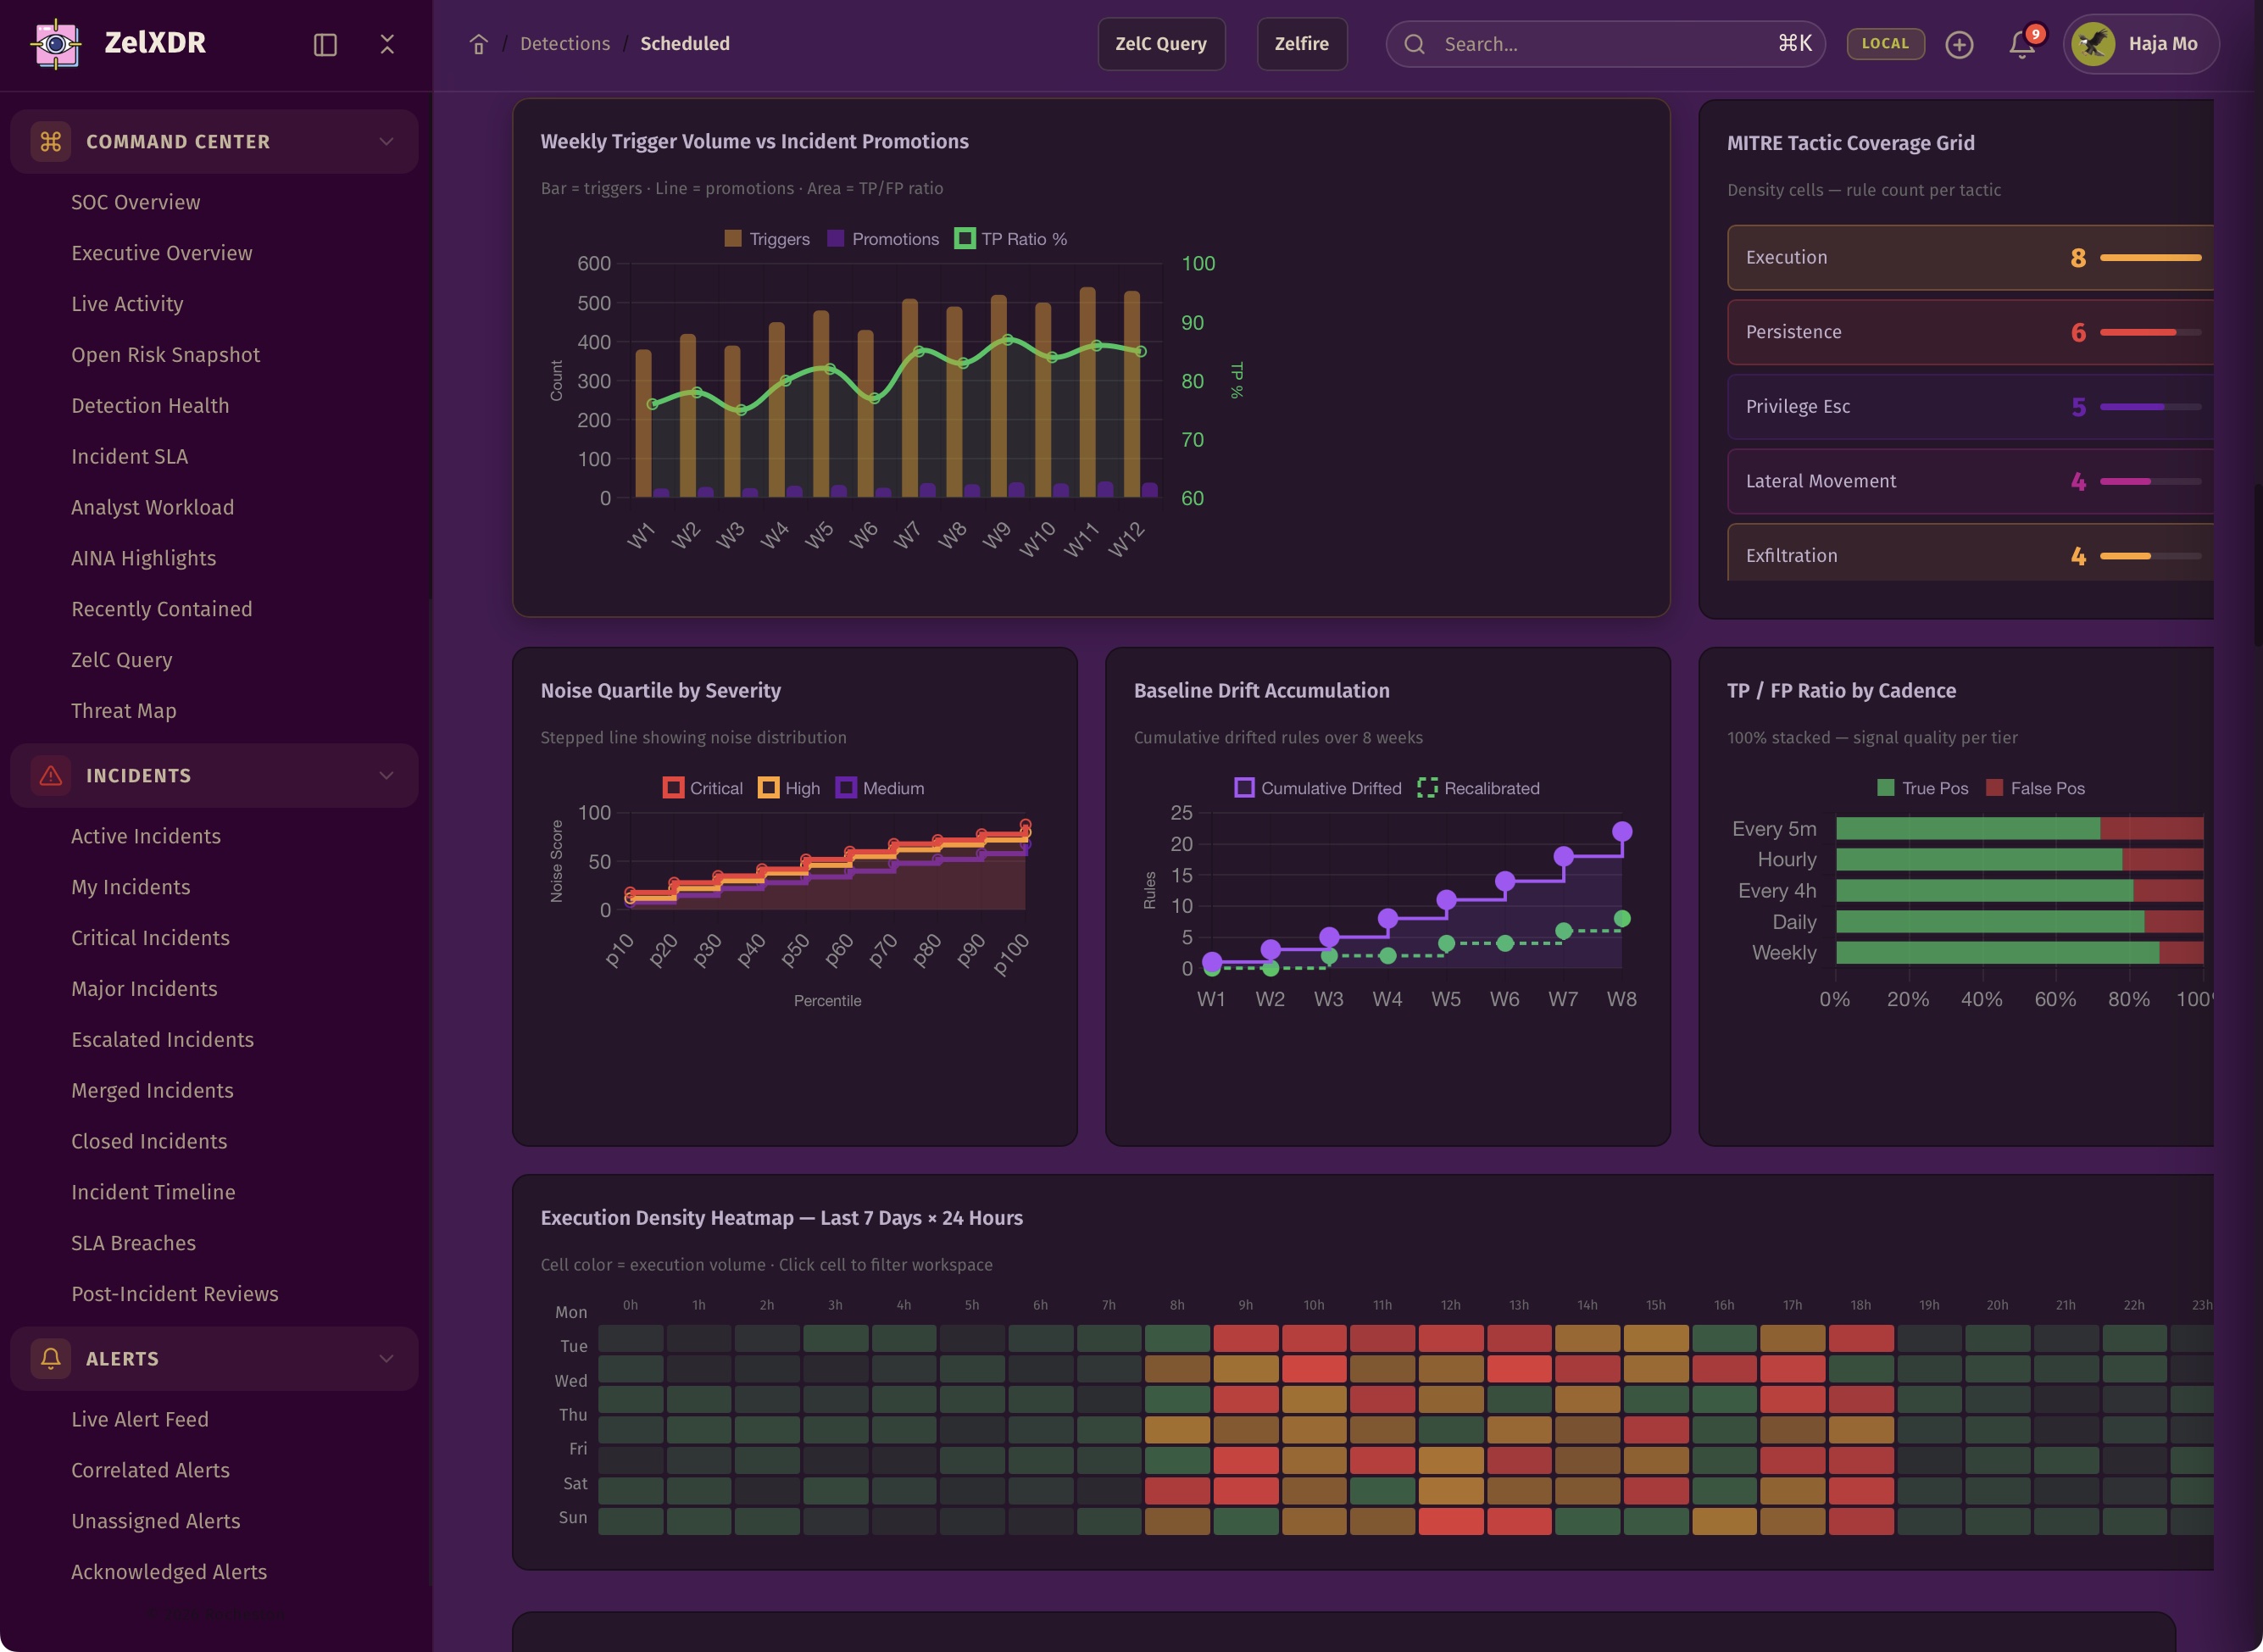
ZelXDR supports scheduled detections that run reliably across defined cadences, ensuring periodic visibility into behaviors, exposures, and patterns that require time-based analysis.
Consistency in detection is its own form of defense.
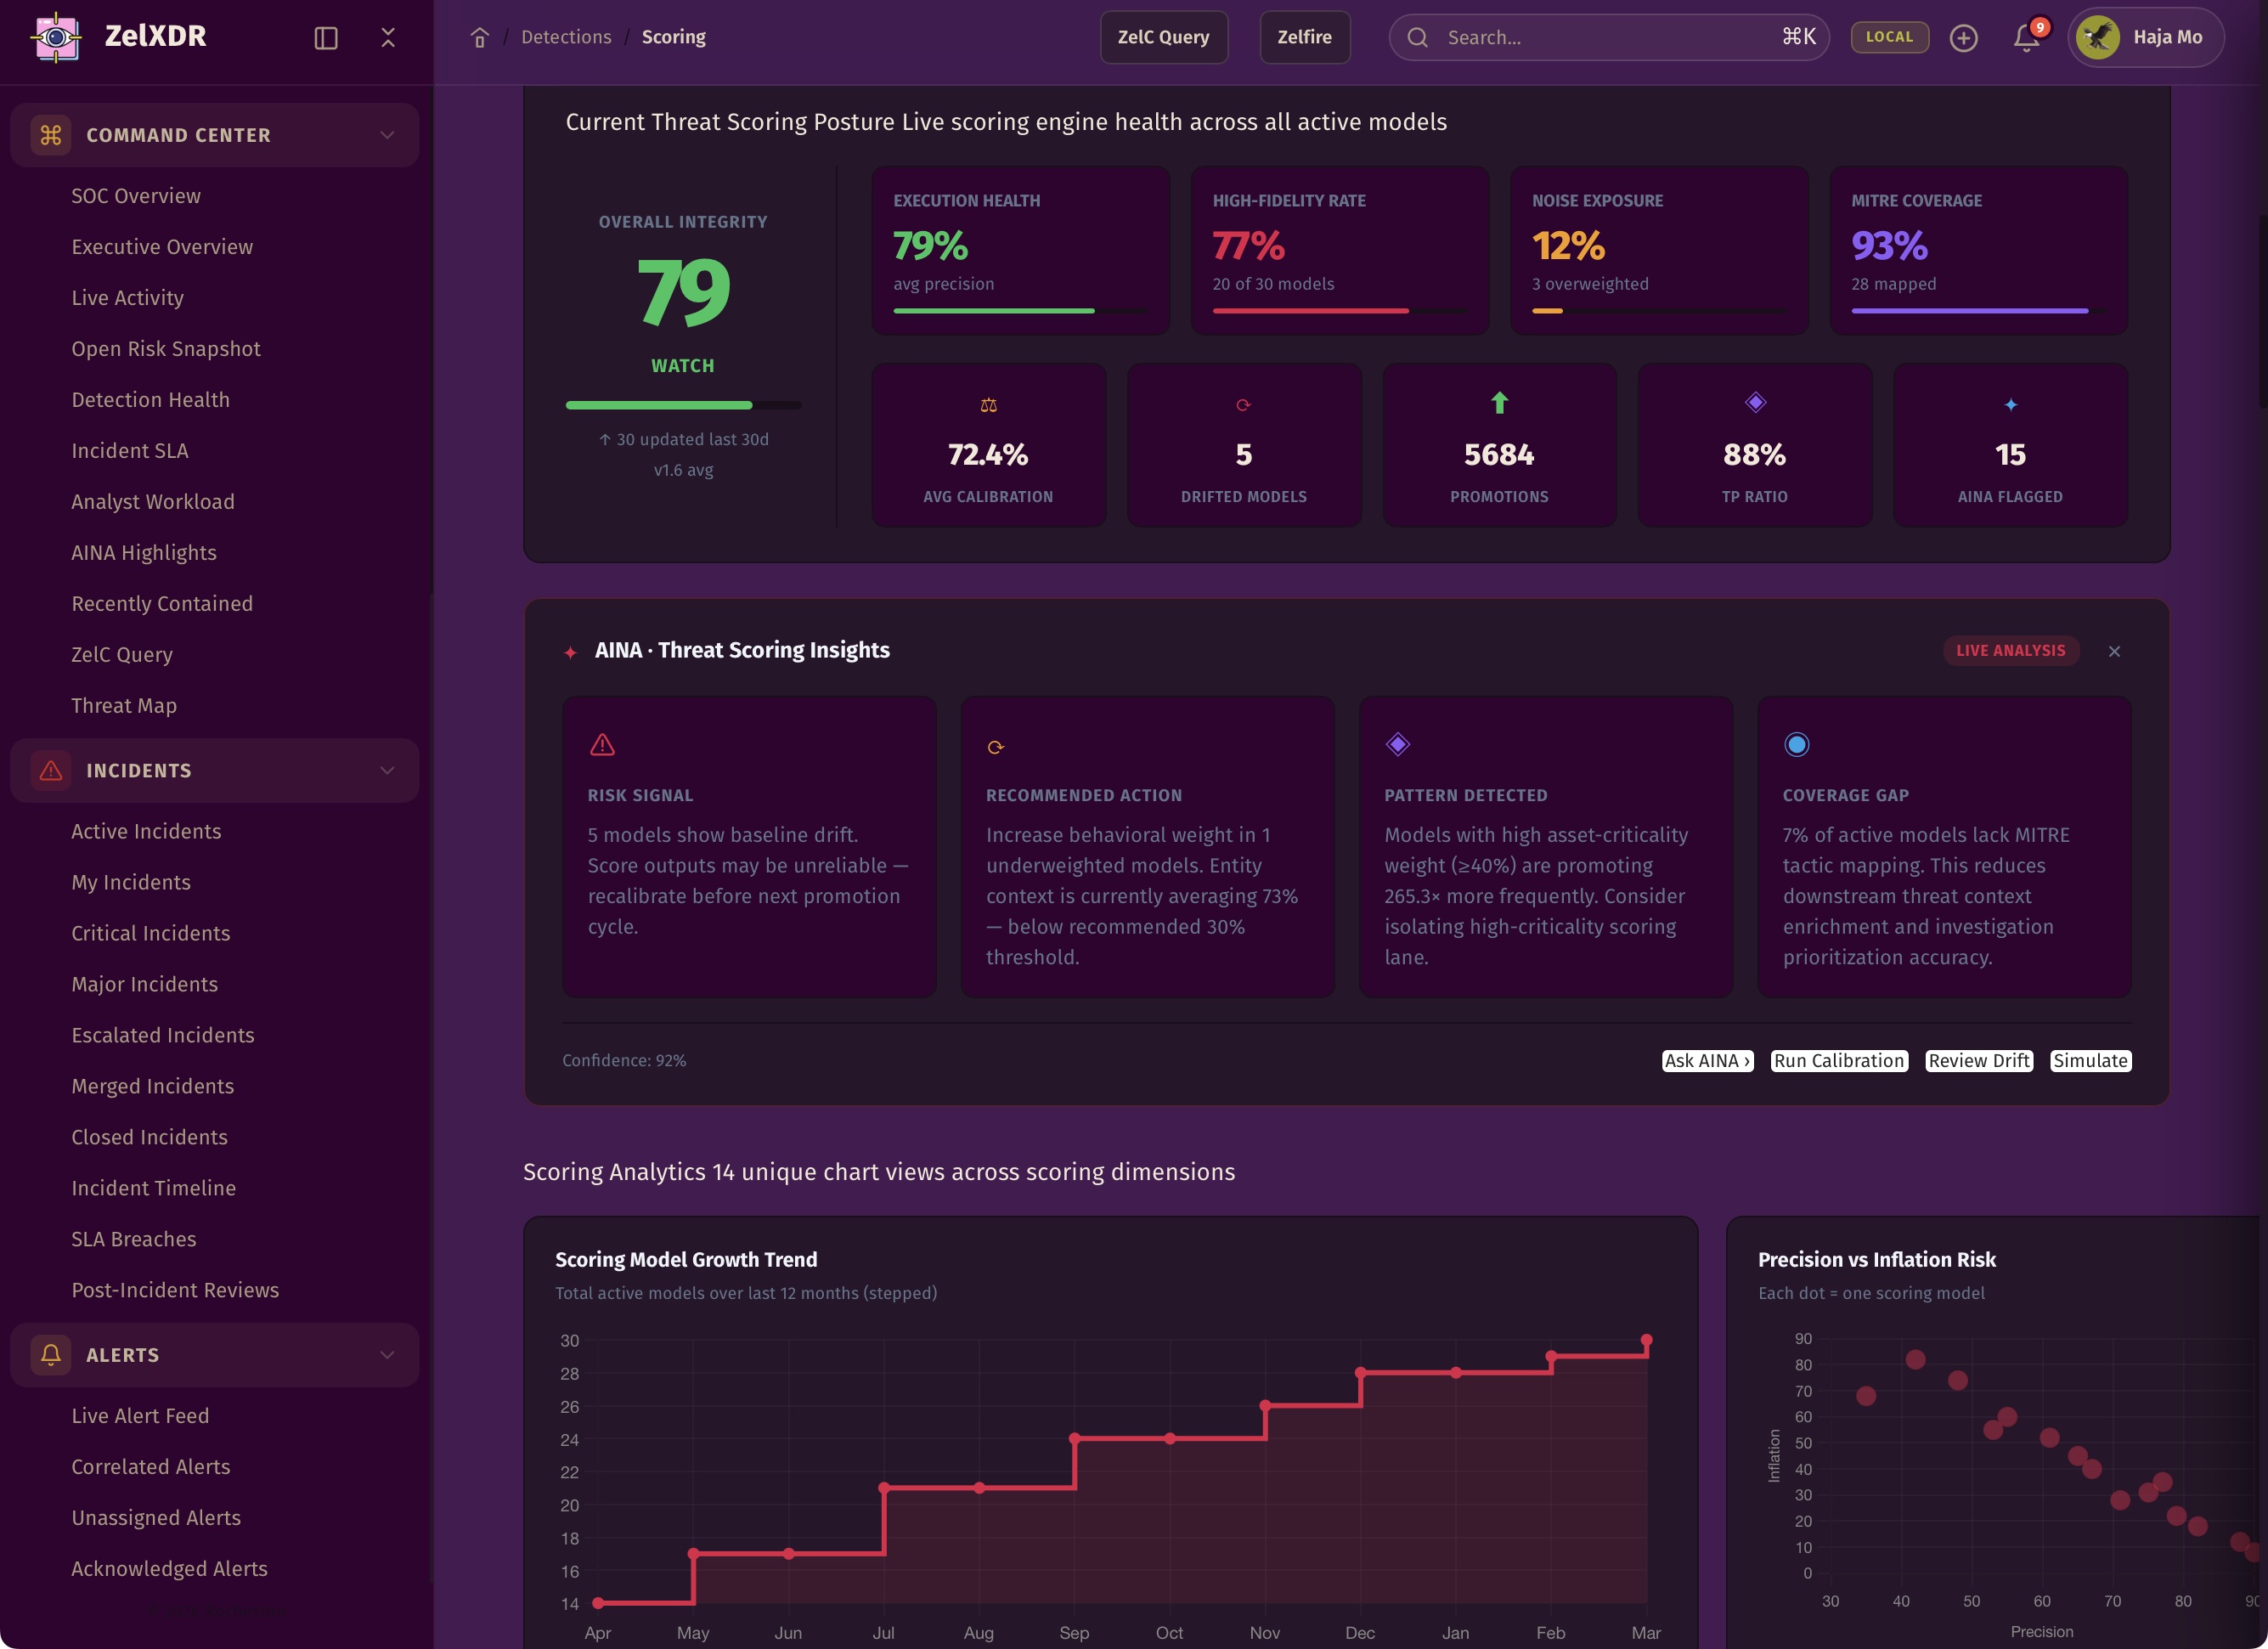
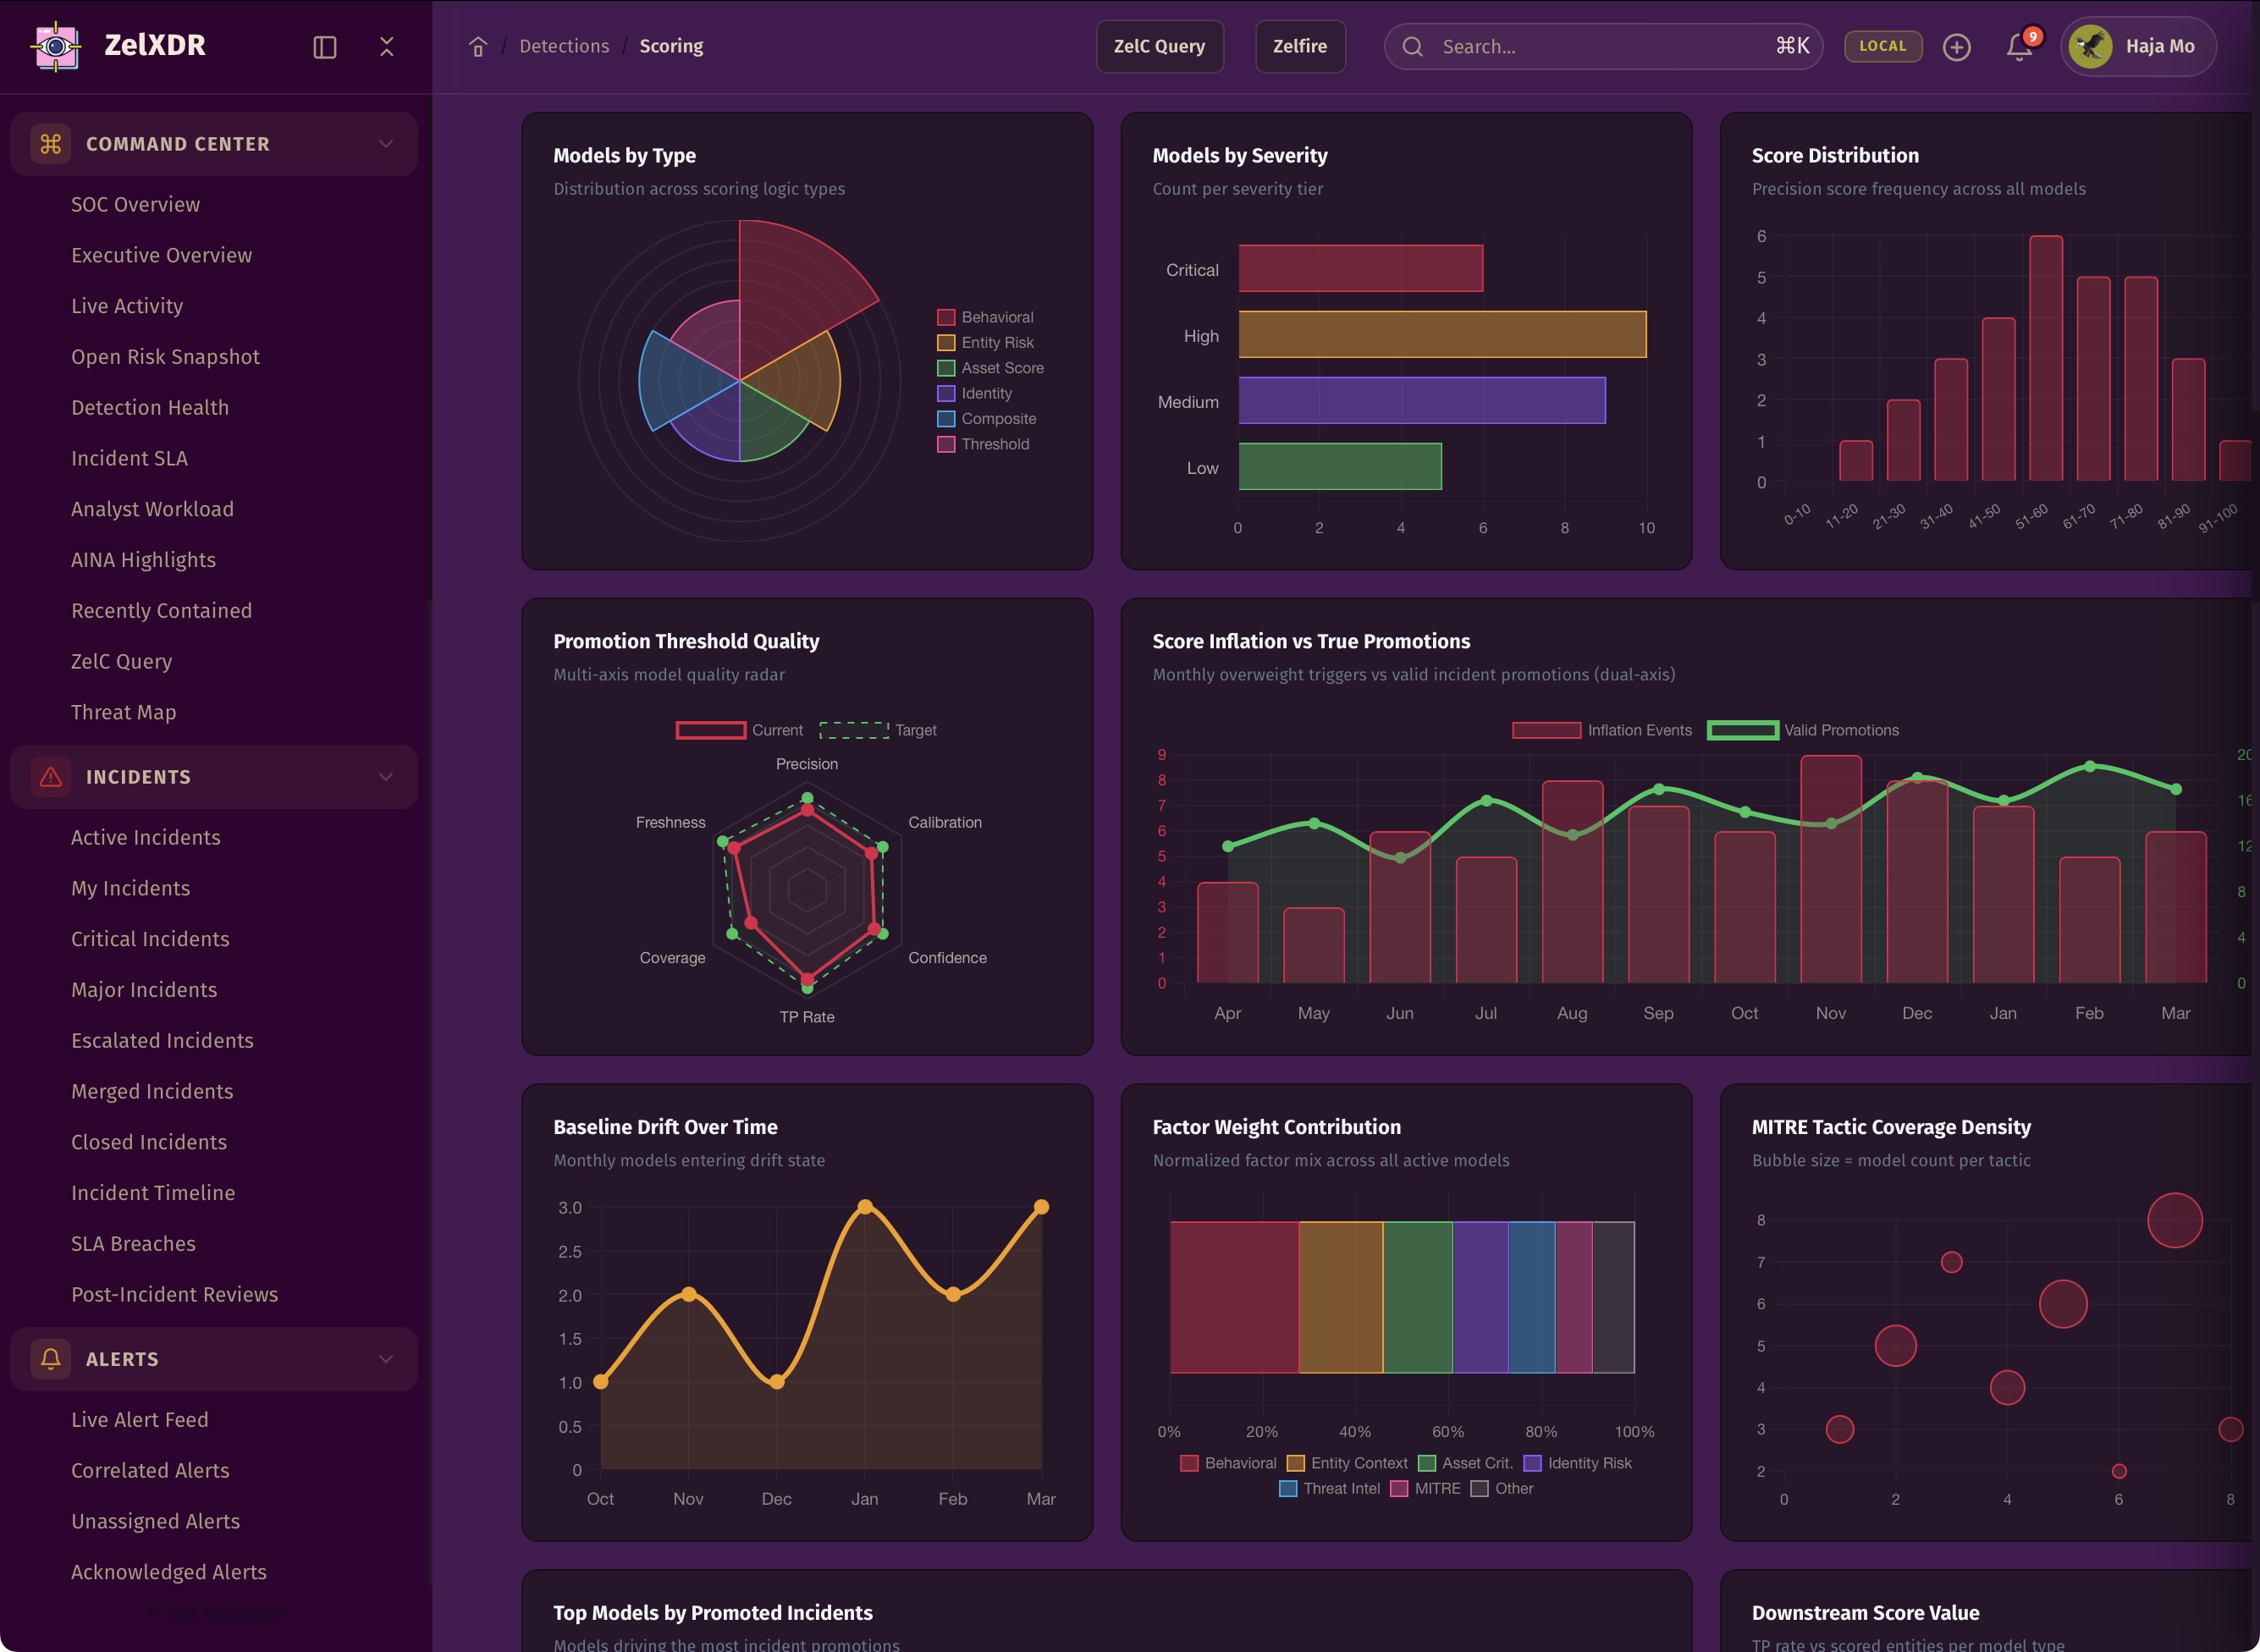
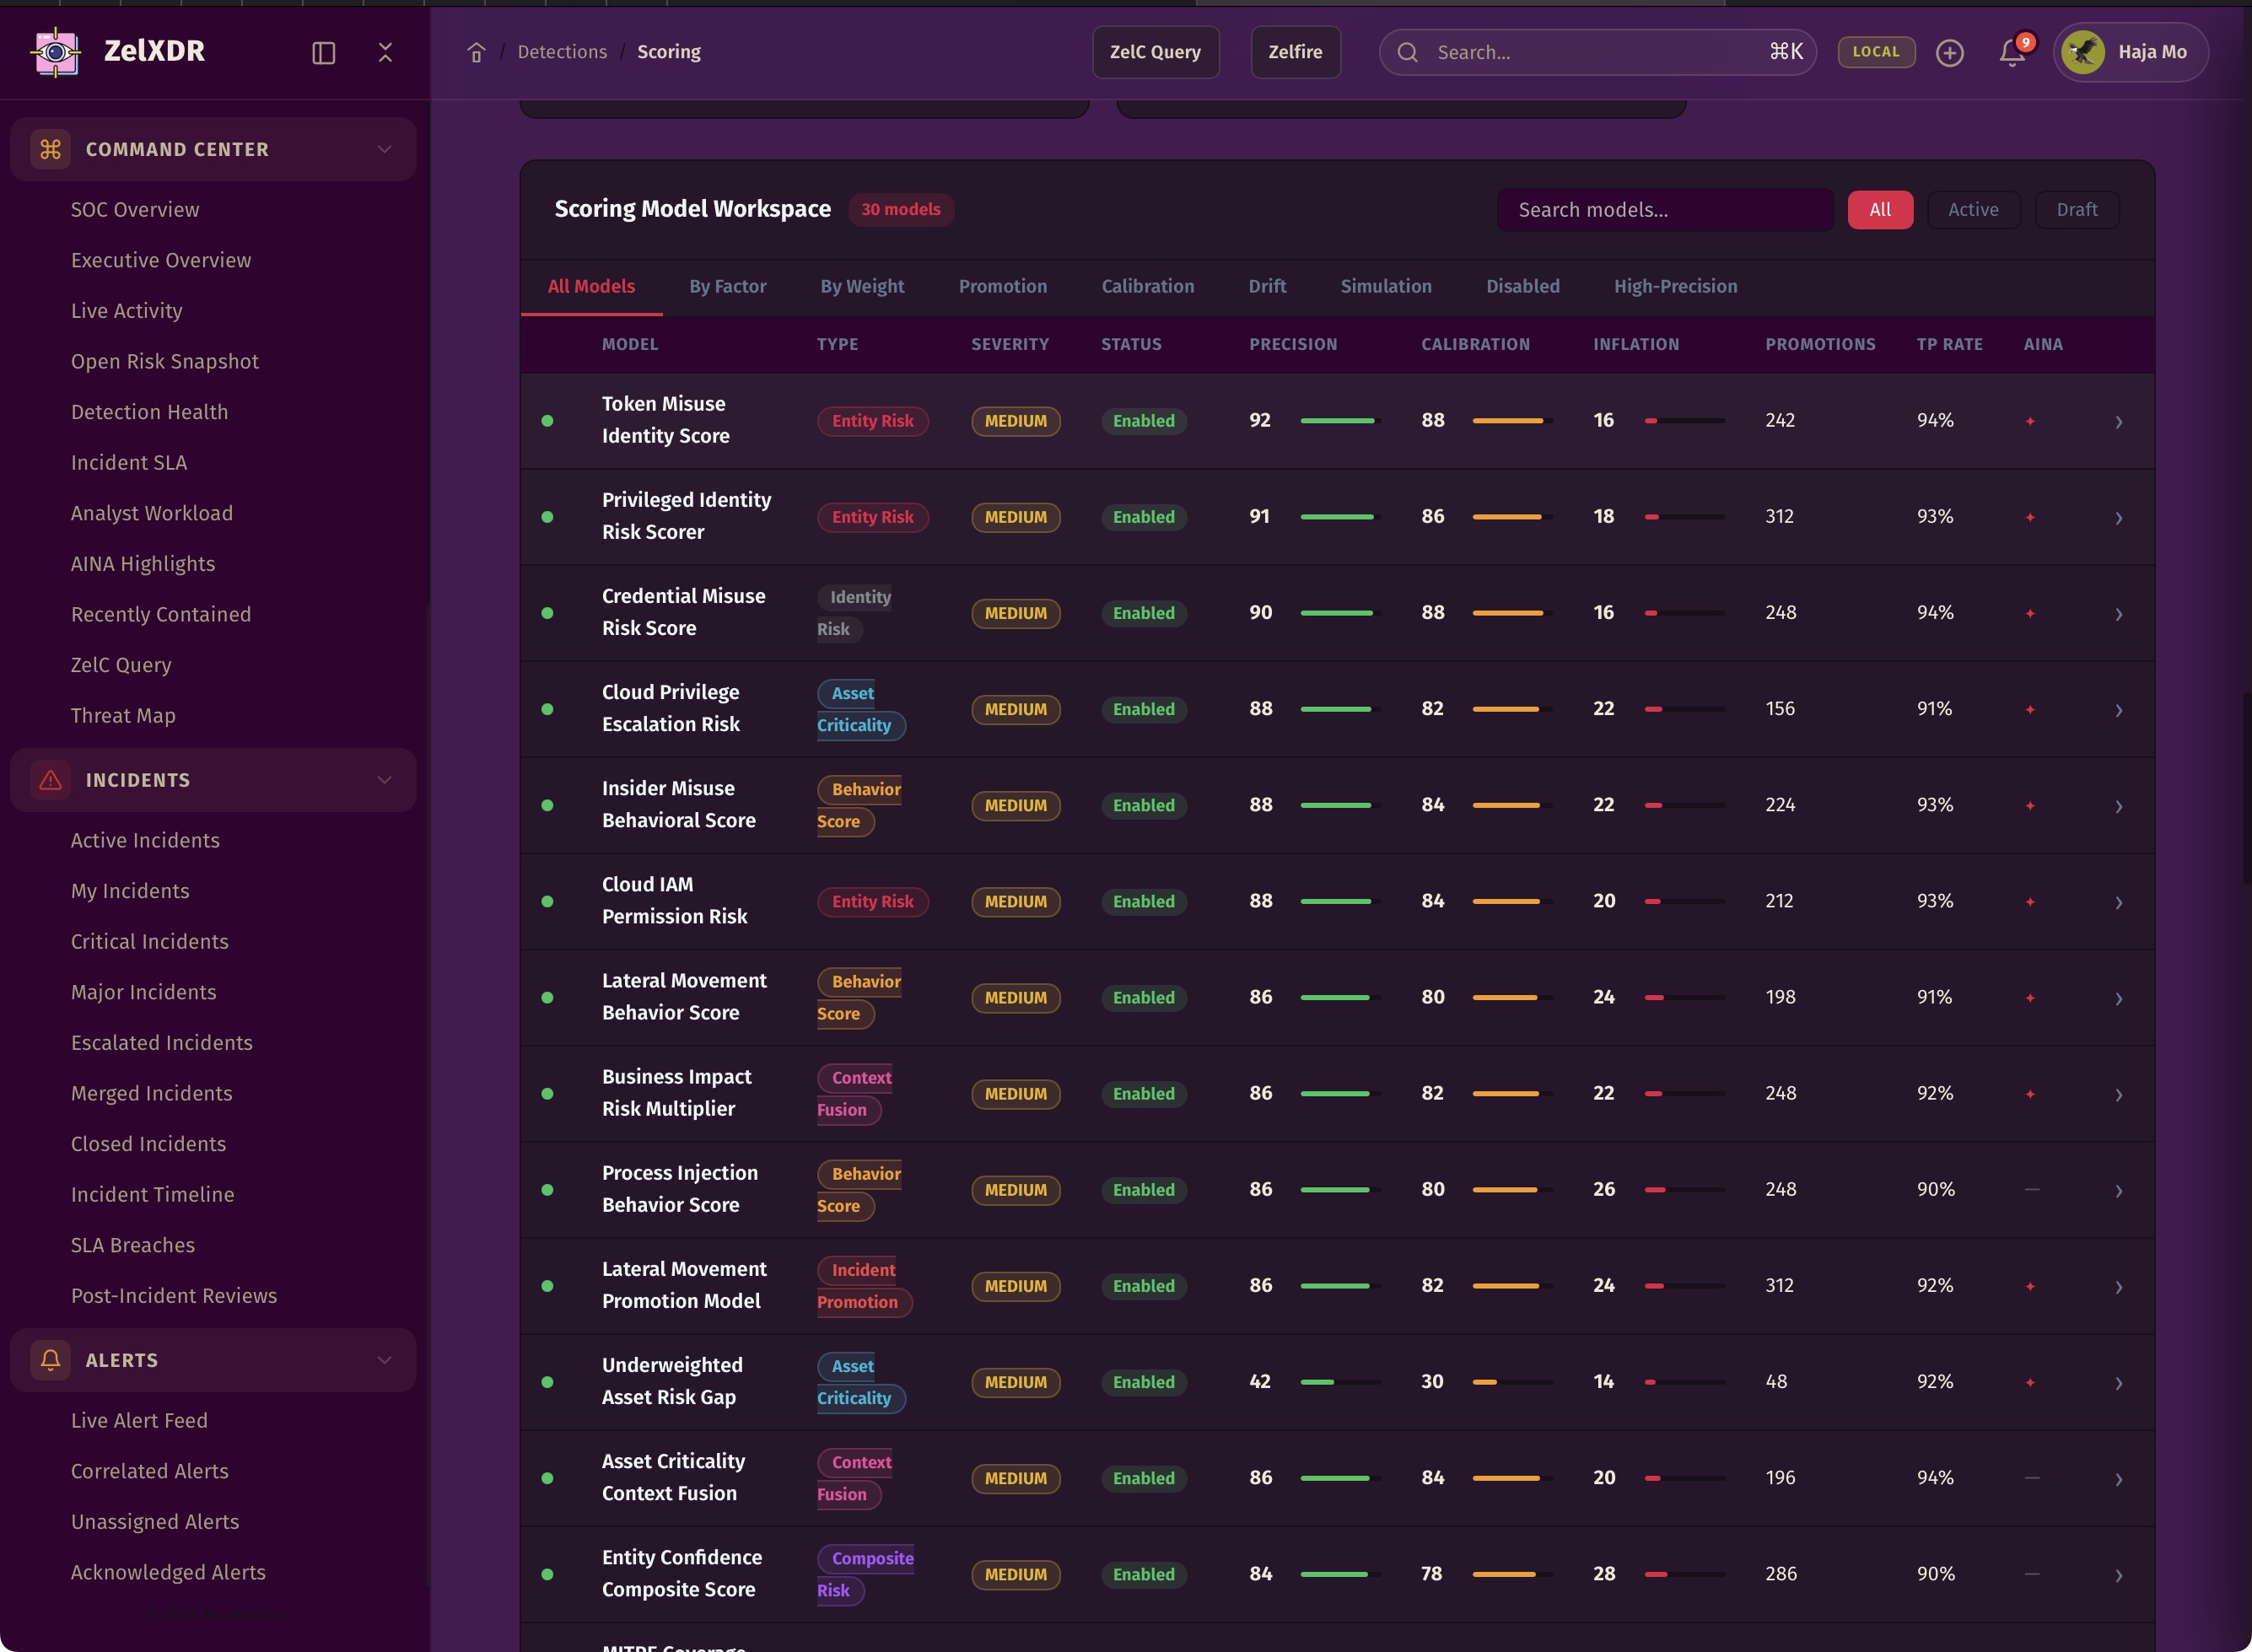
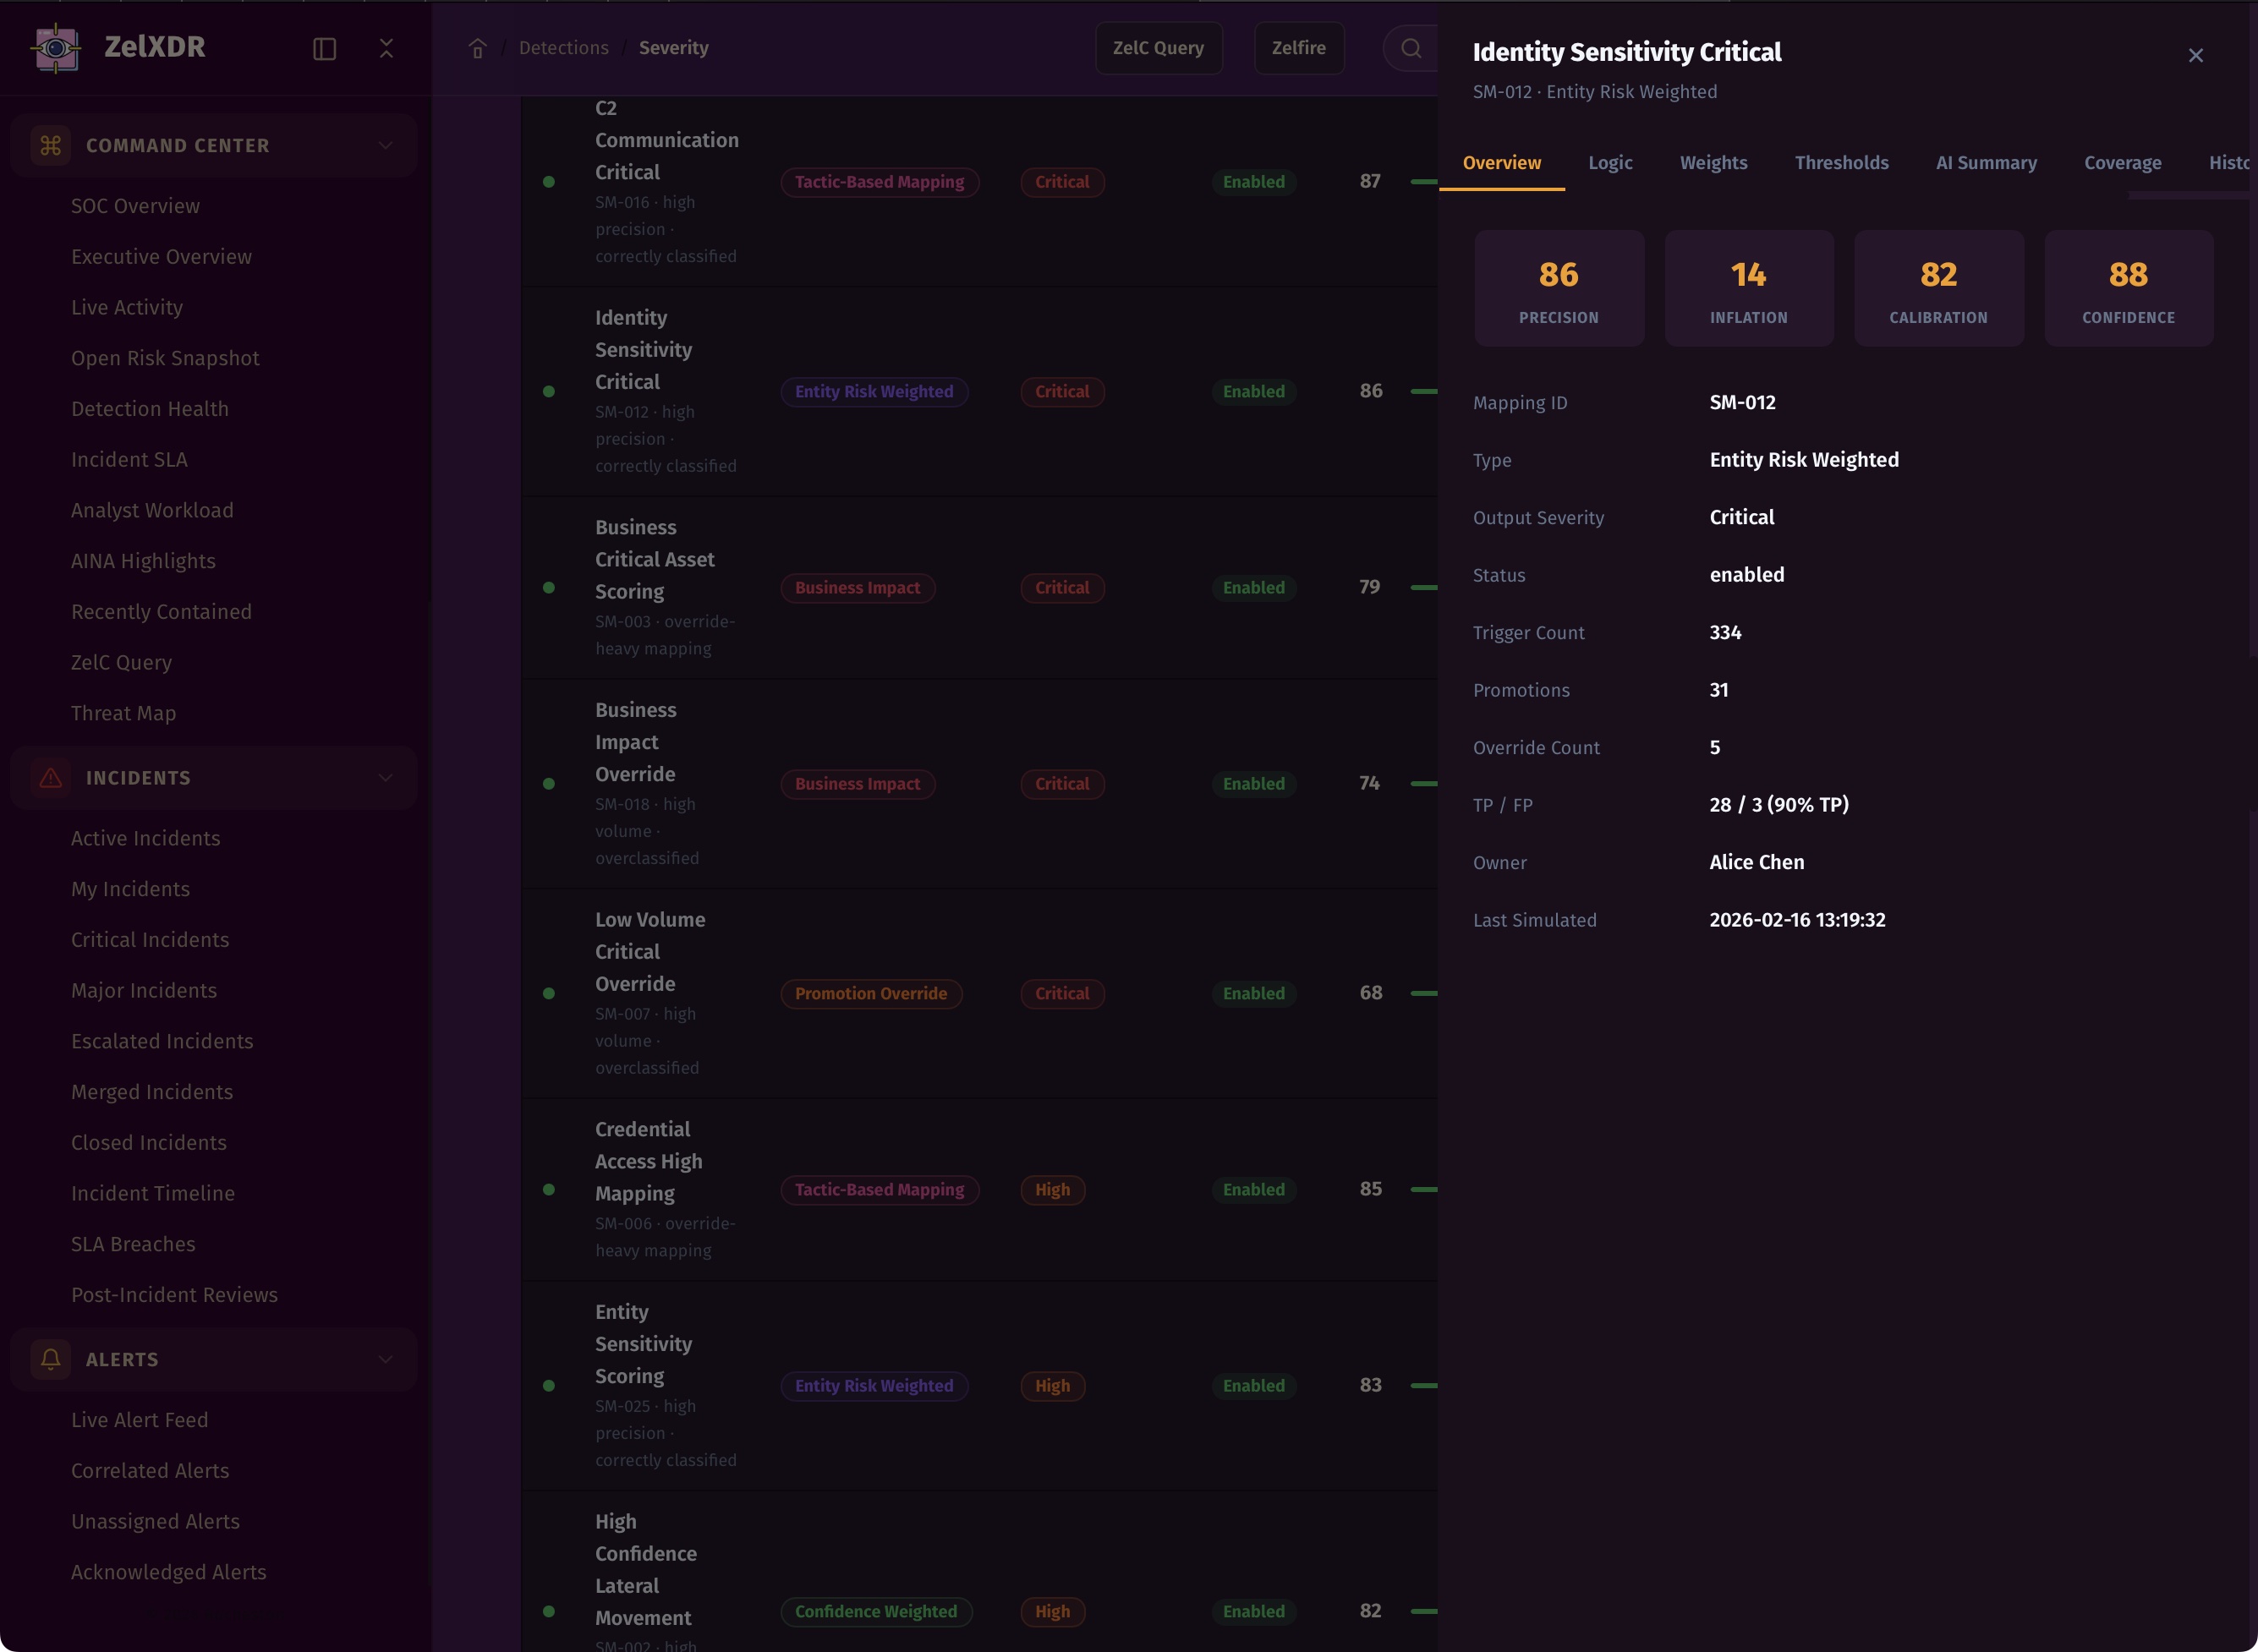
ZelXDR uses weighted scoring models to combine confidence, business impact, asset criticality, identity sensitivity, and evidence depth into smarter prioritization.
Priority should be earned by context, not assigned by habit.
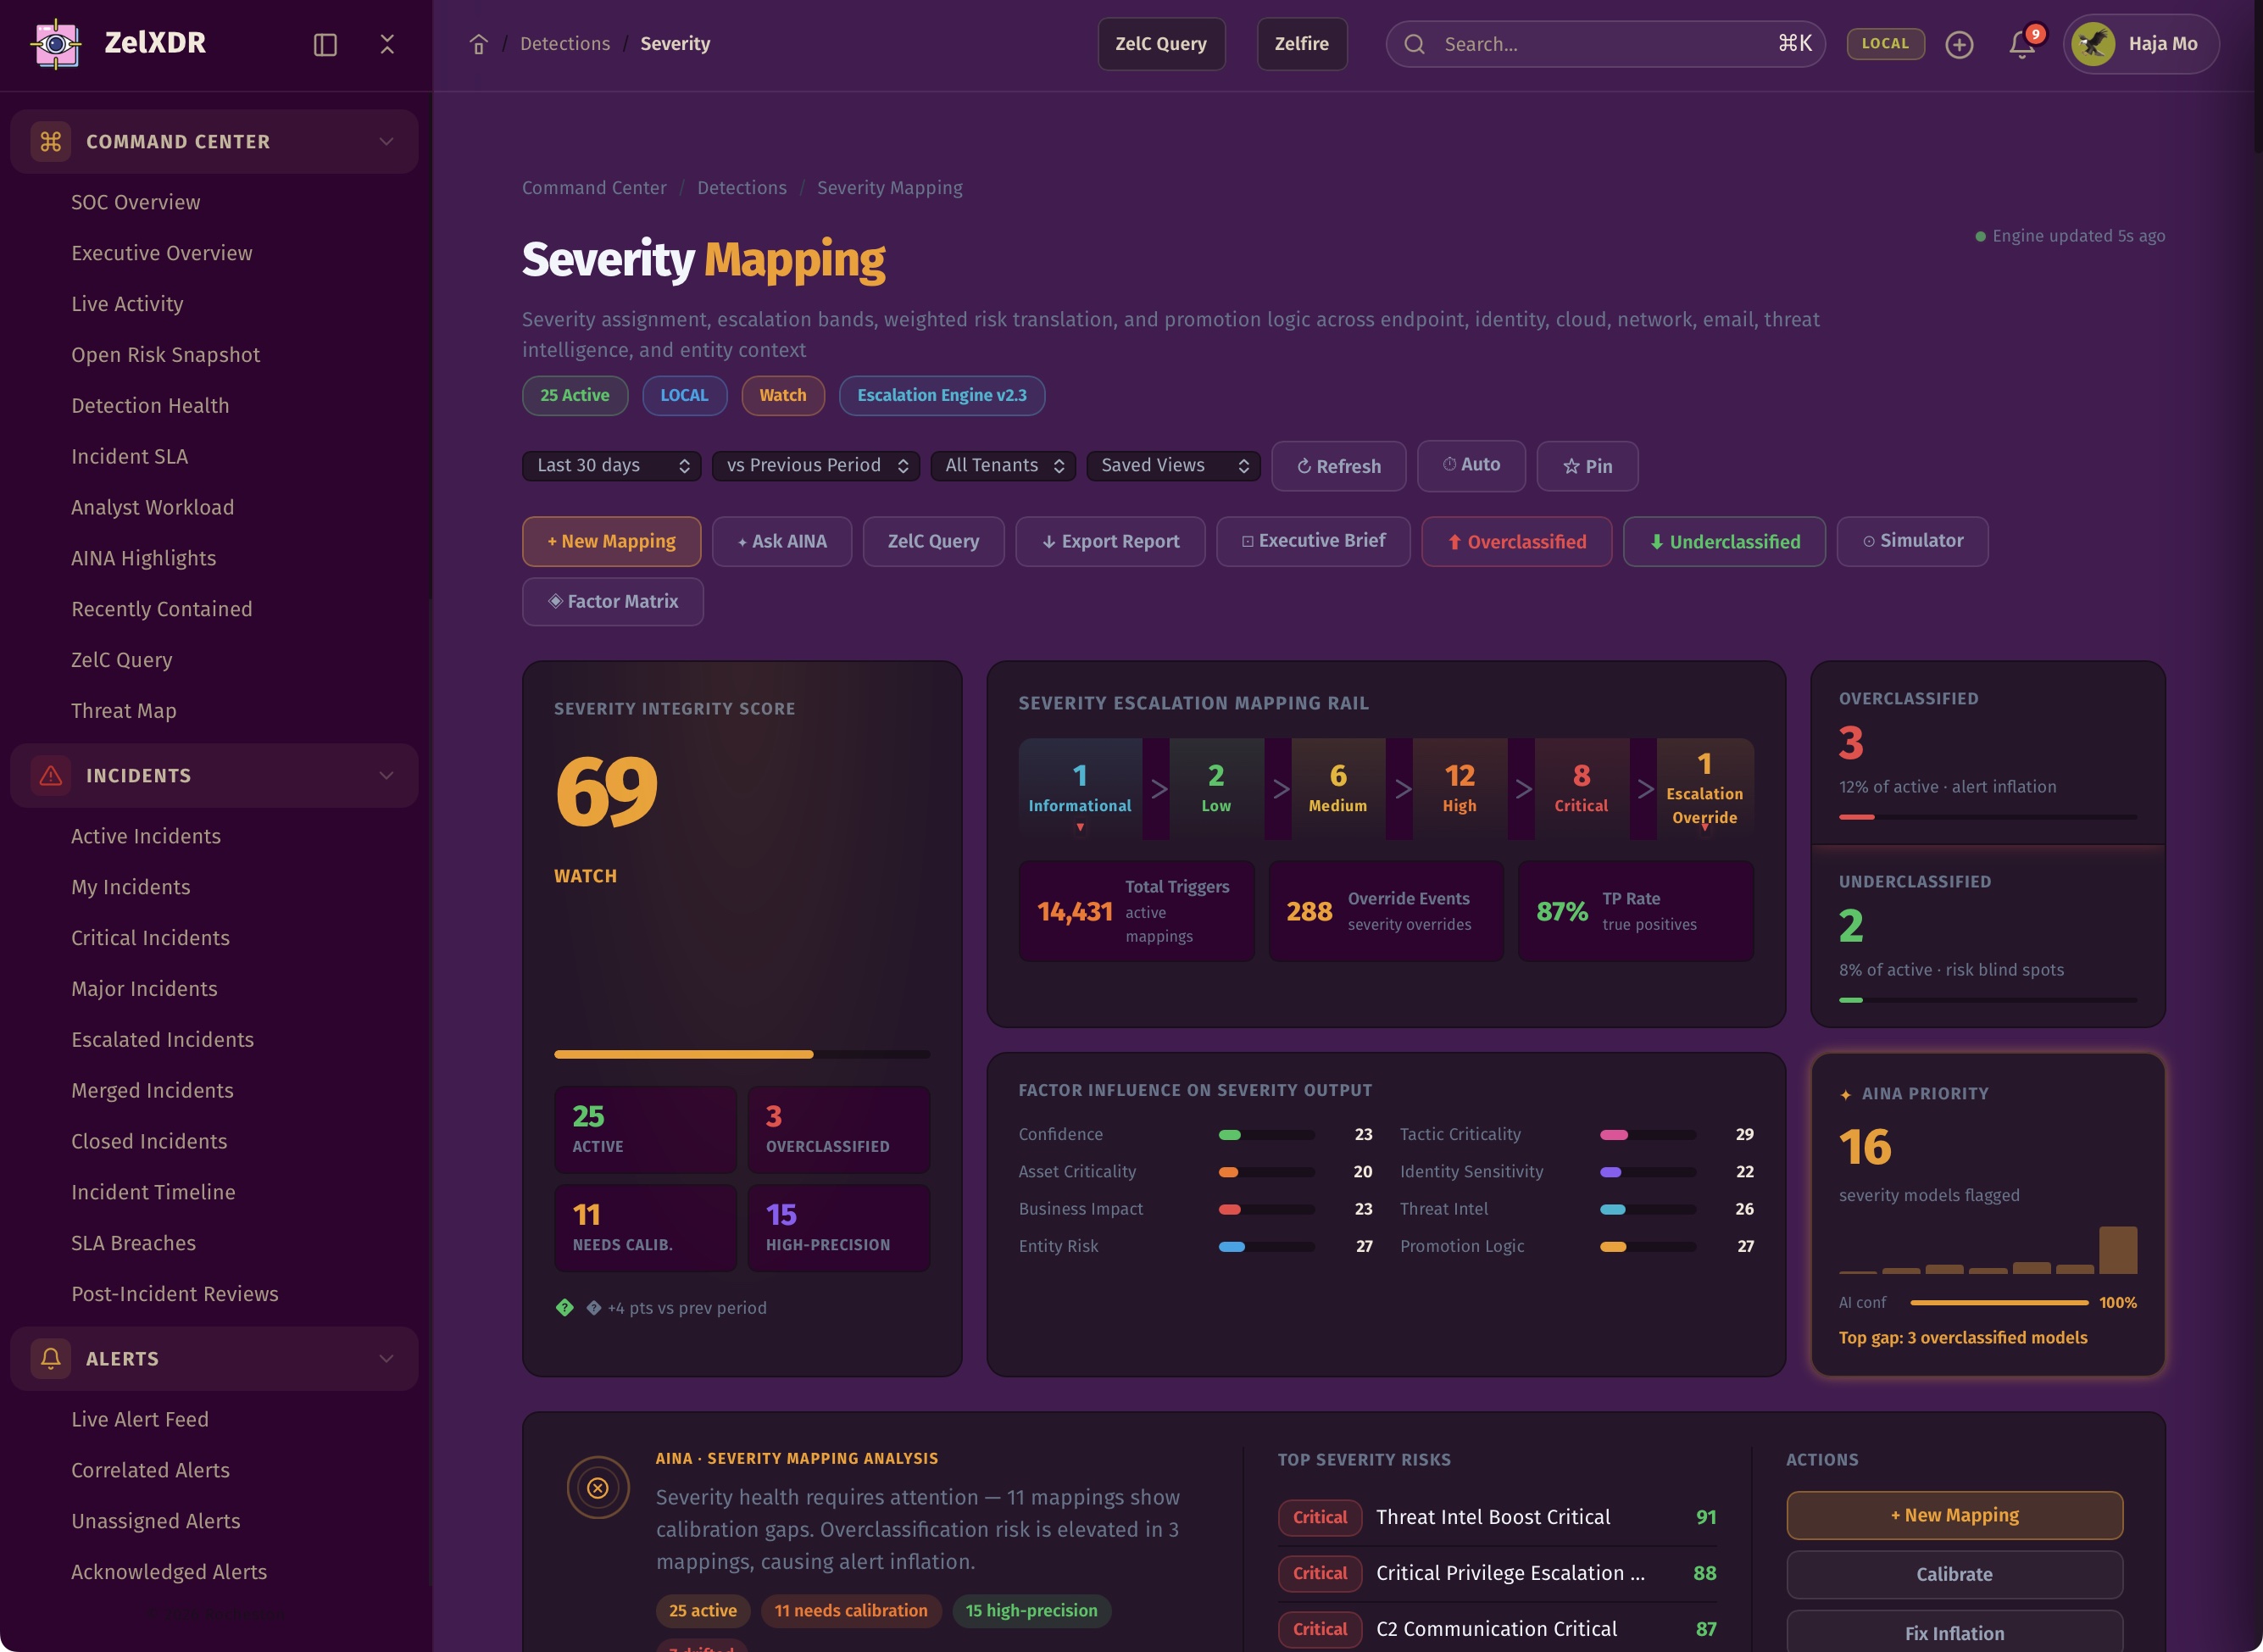
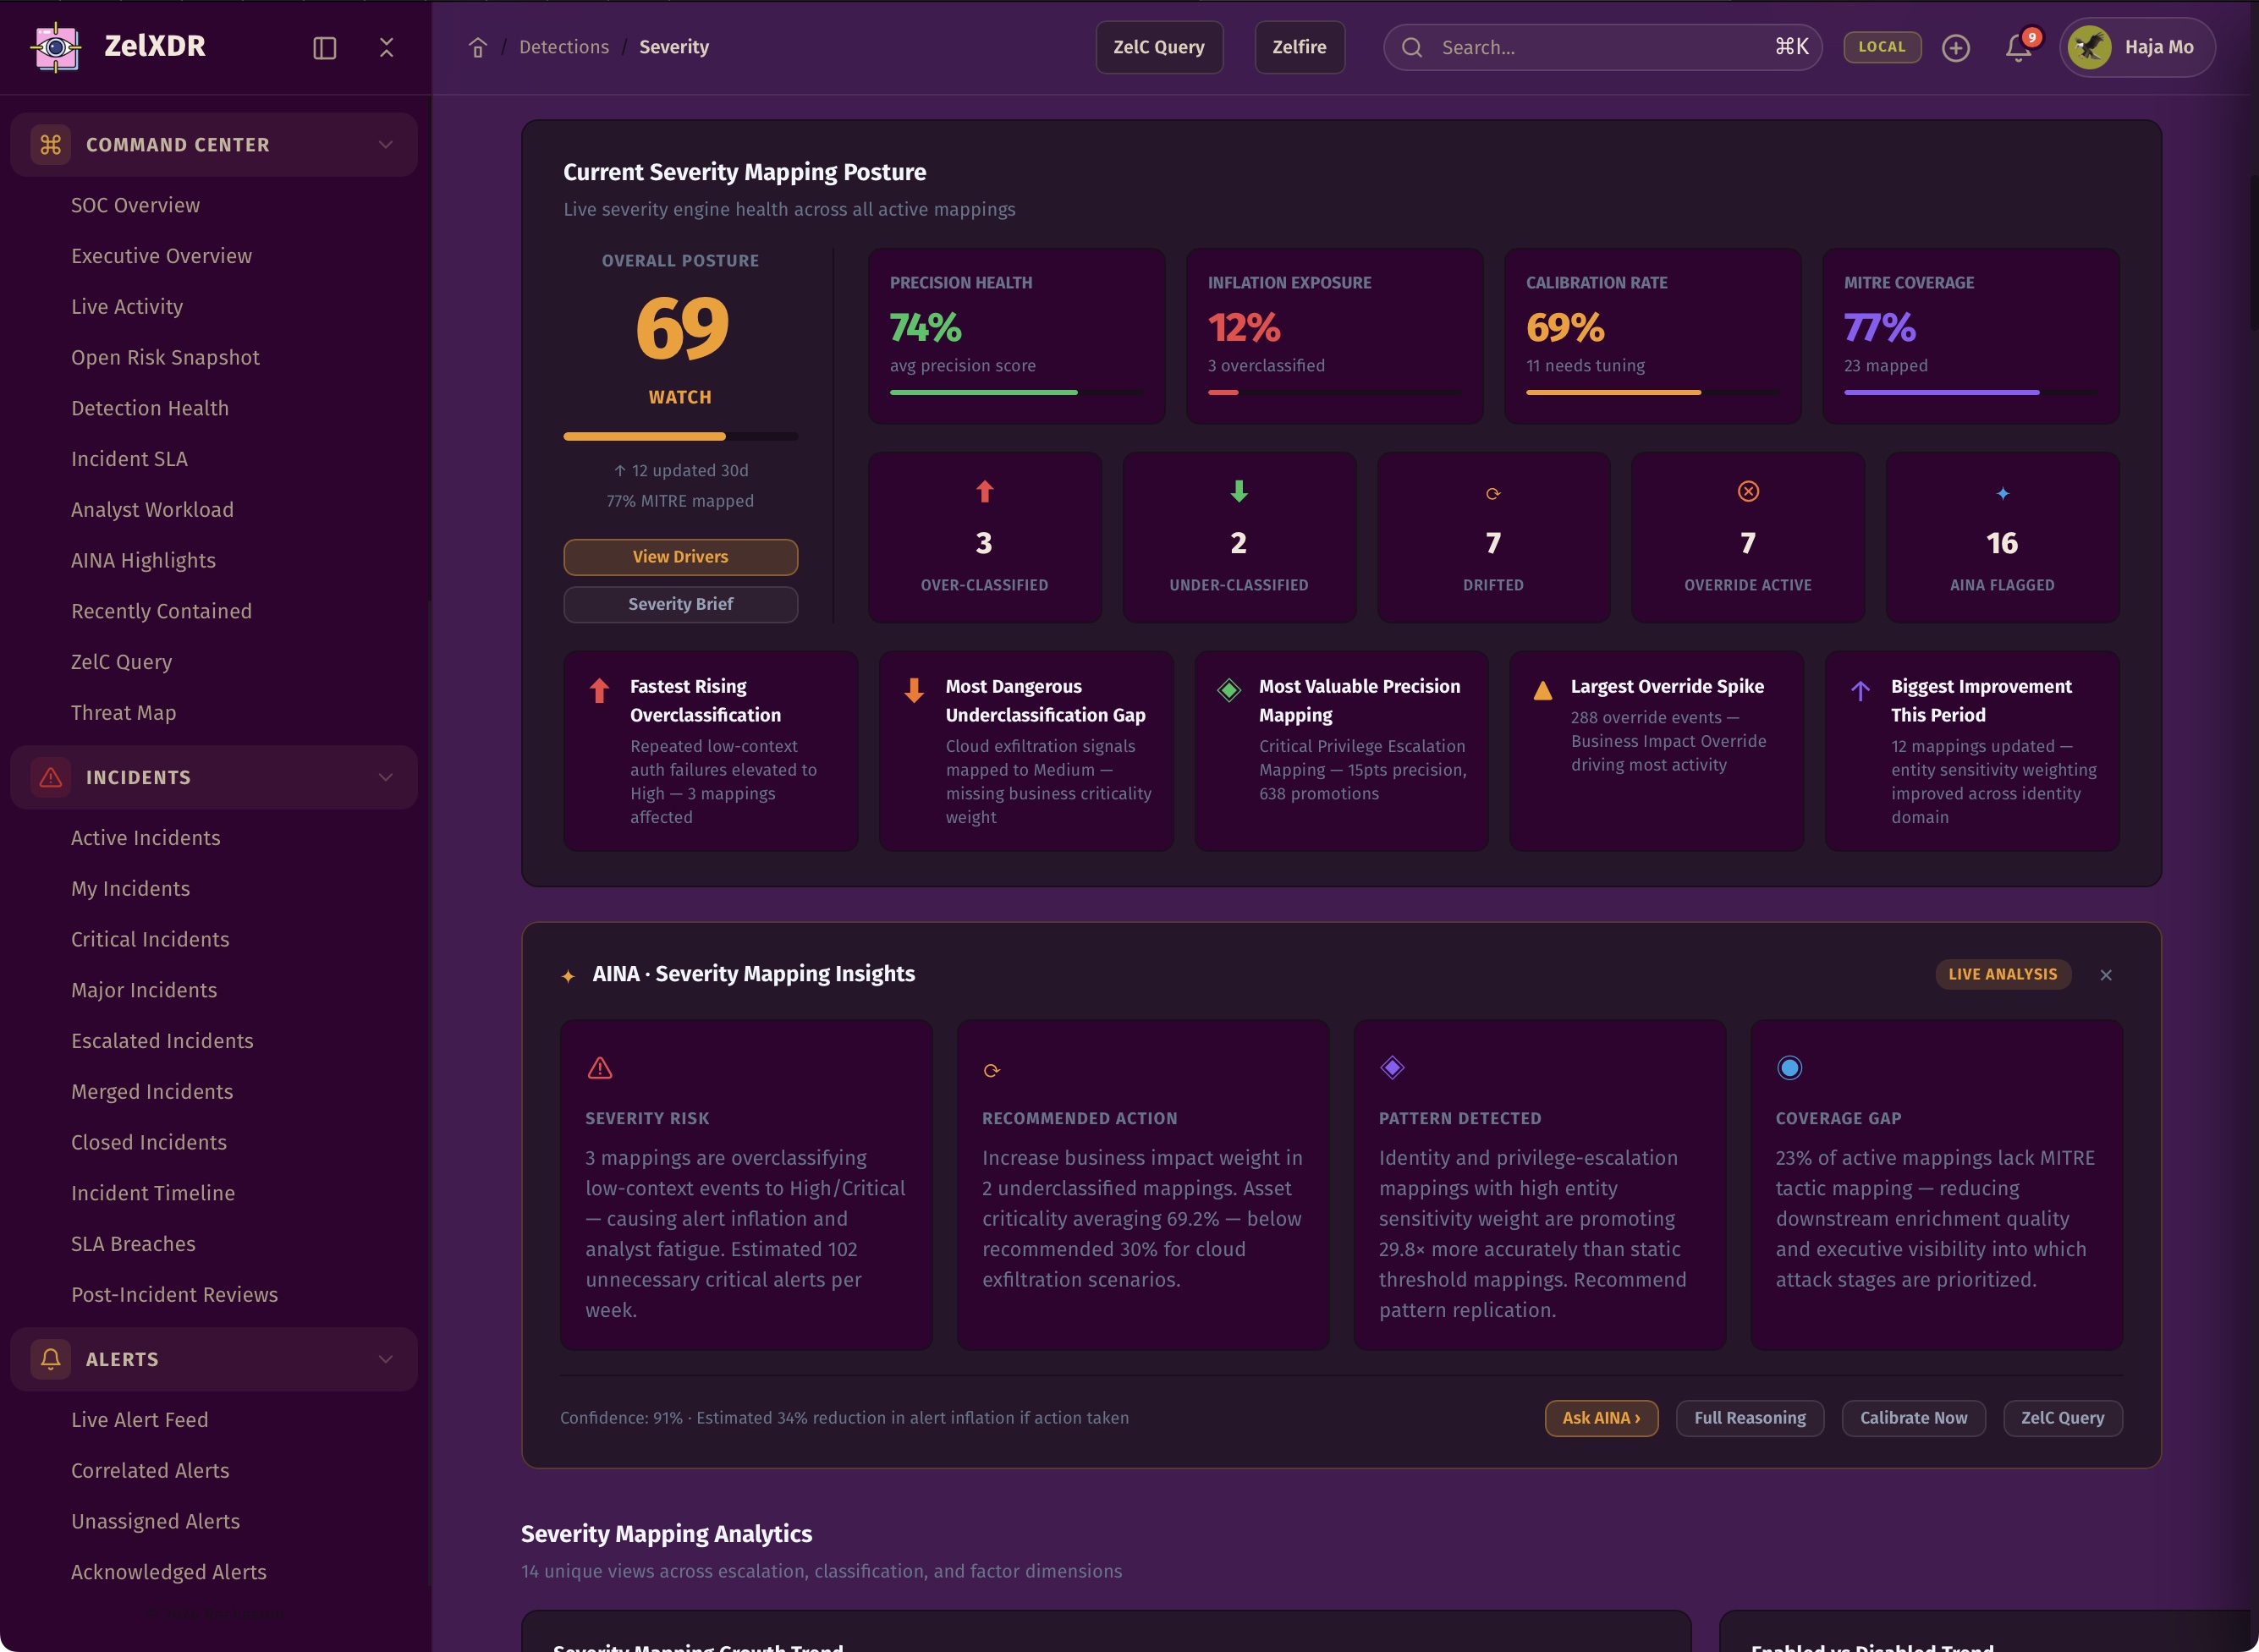
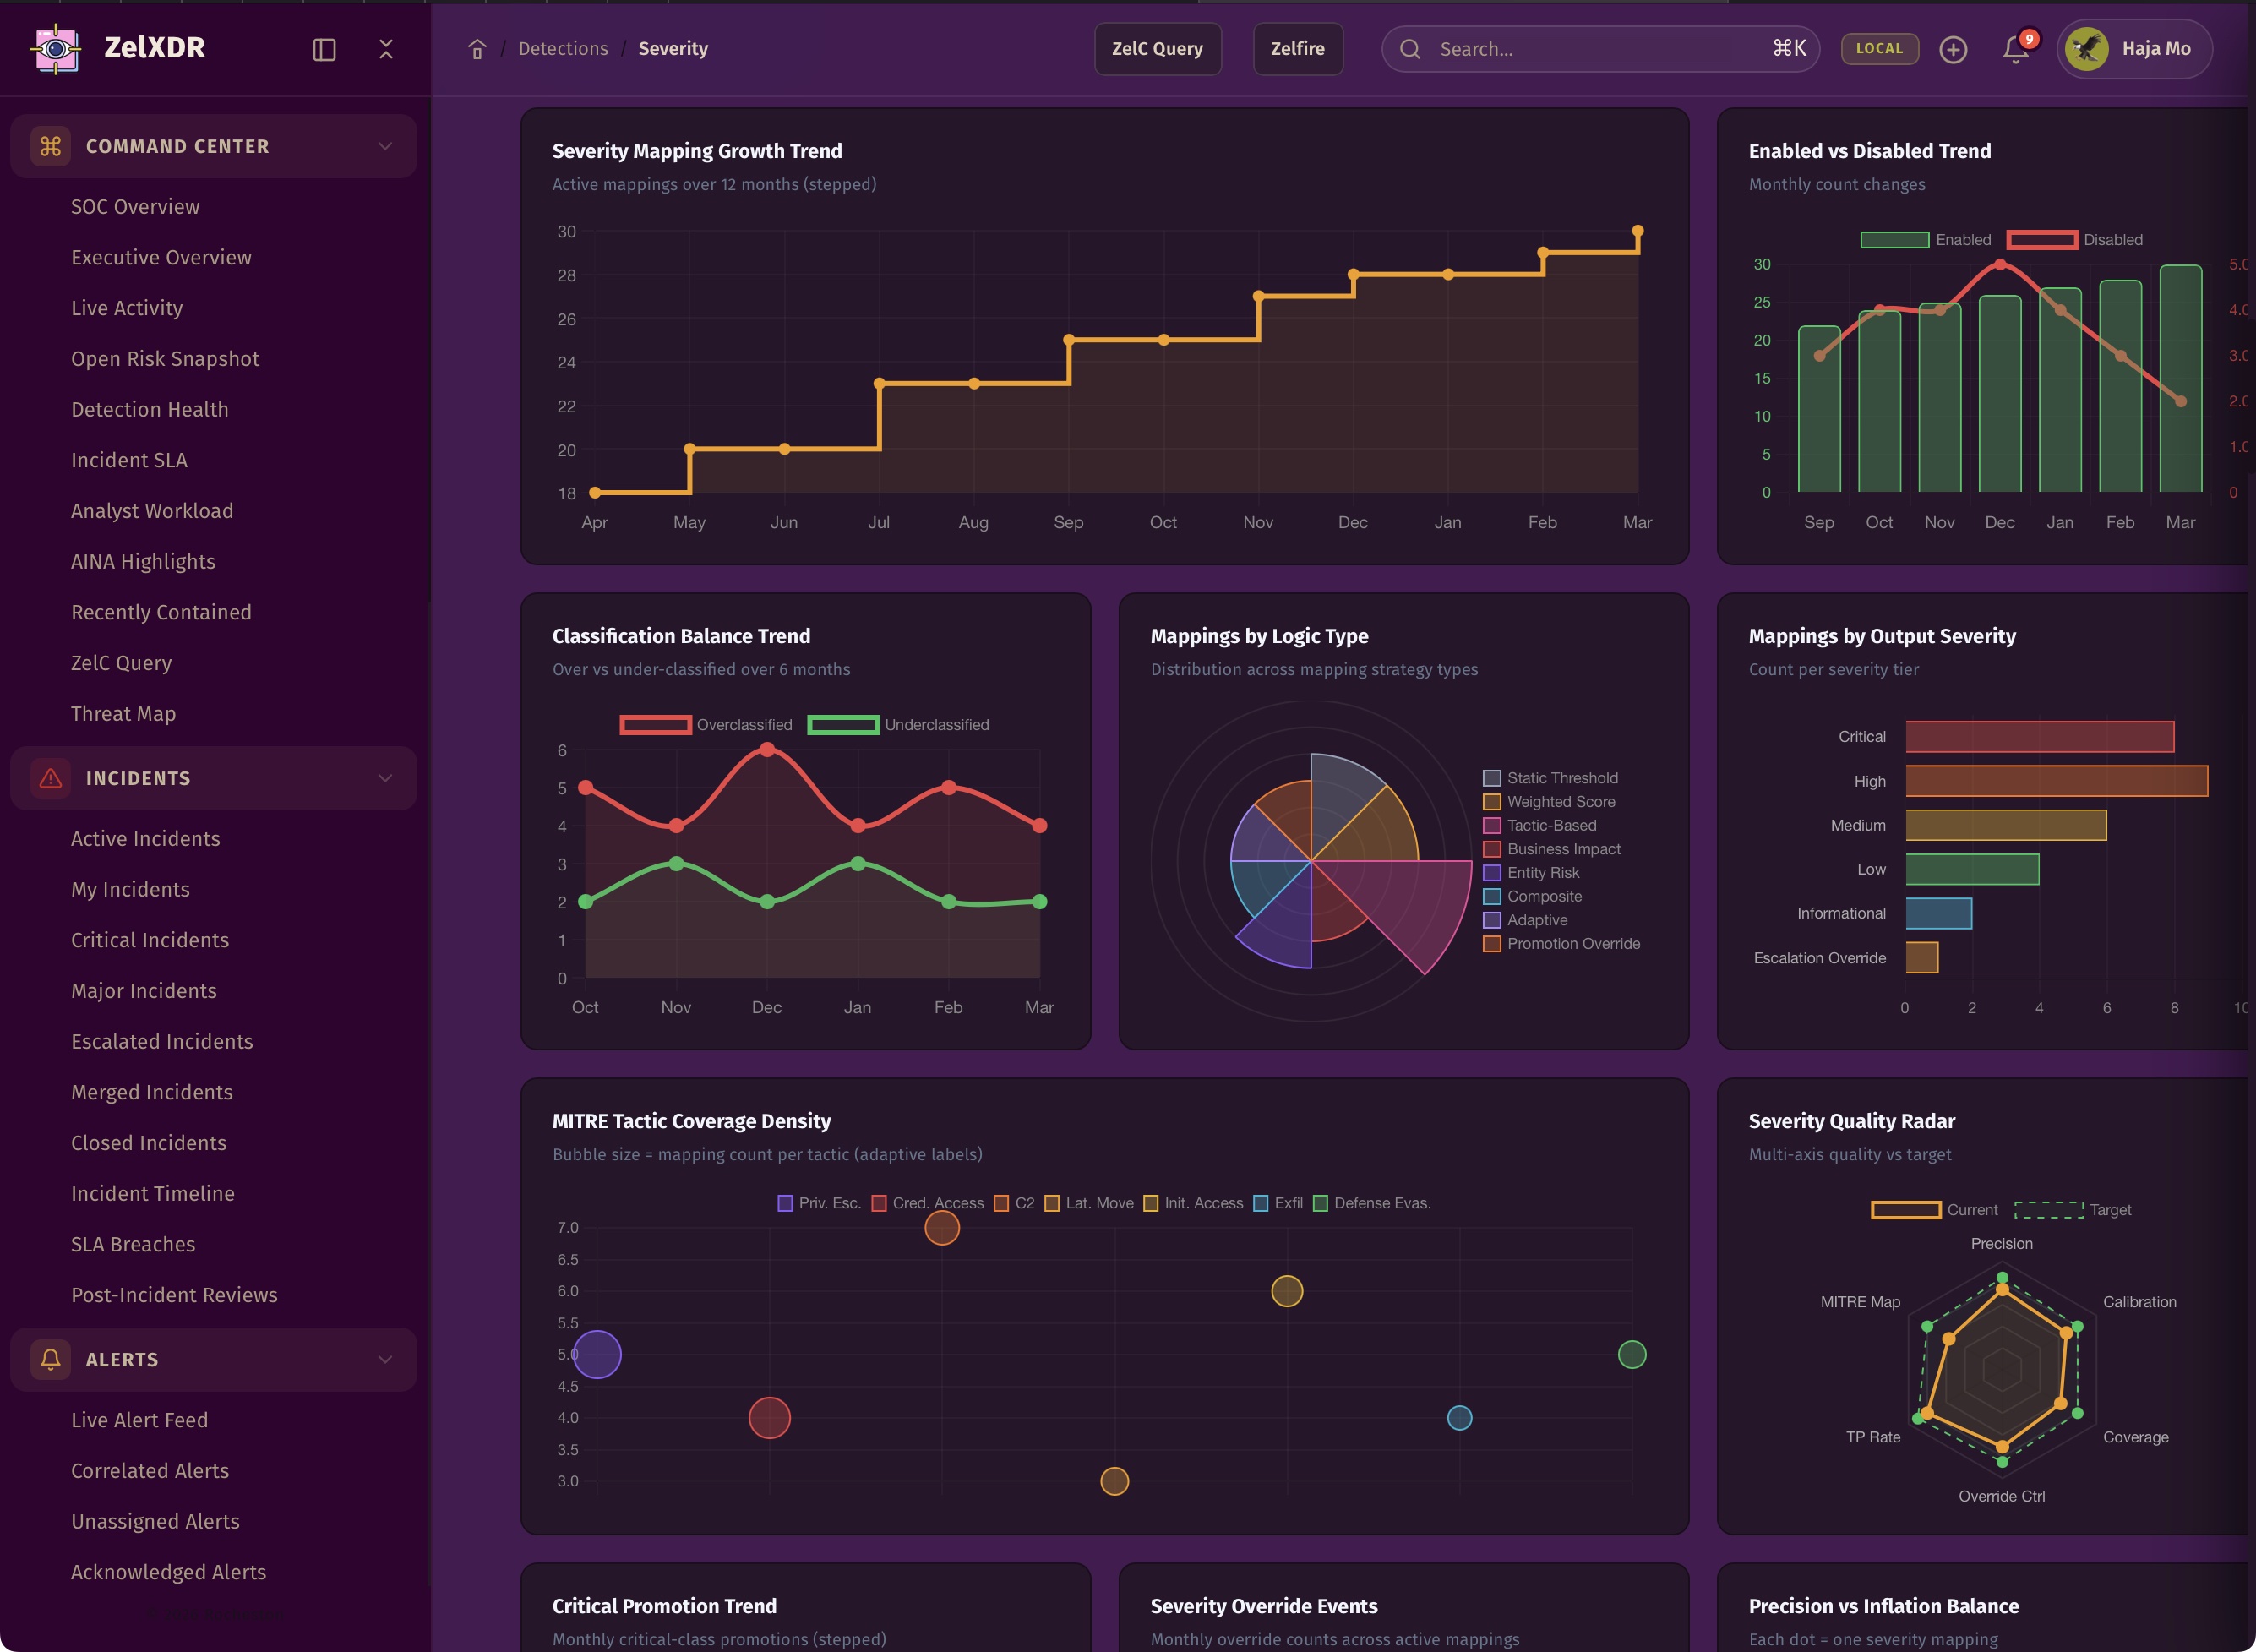
ZelXDR translates detections into clear severity based on signal quality, tactic importance, impact, and operational context, helping teams avoid both overreaction and underreaction.
Severity should describe danger, not just volume.
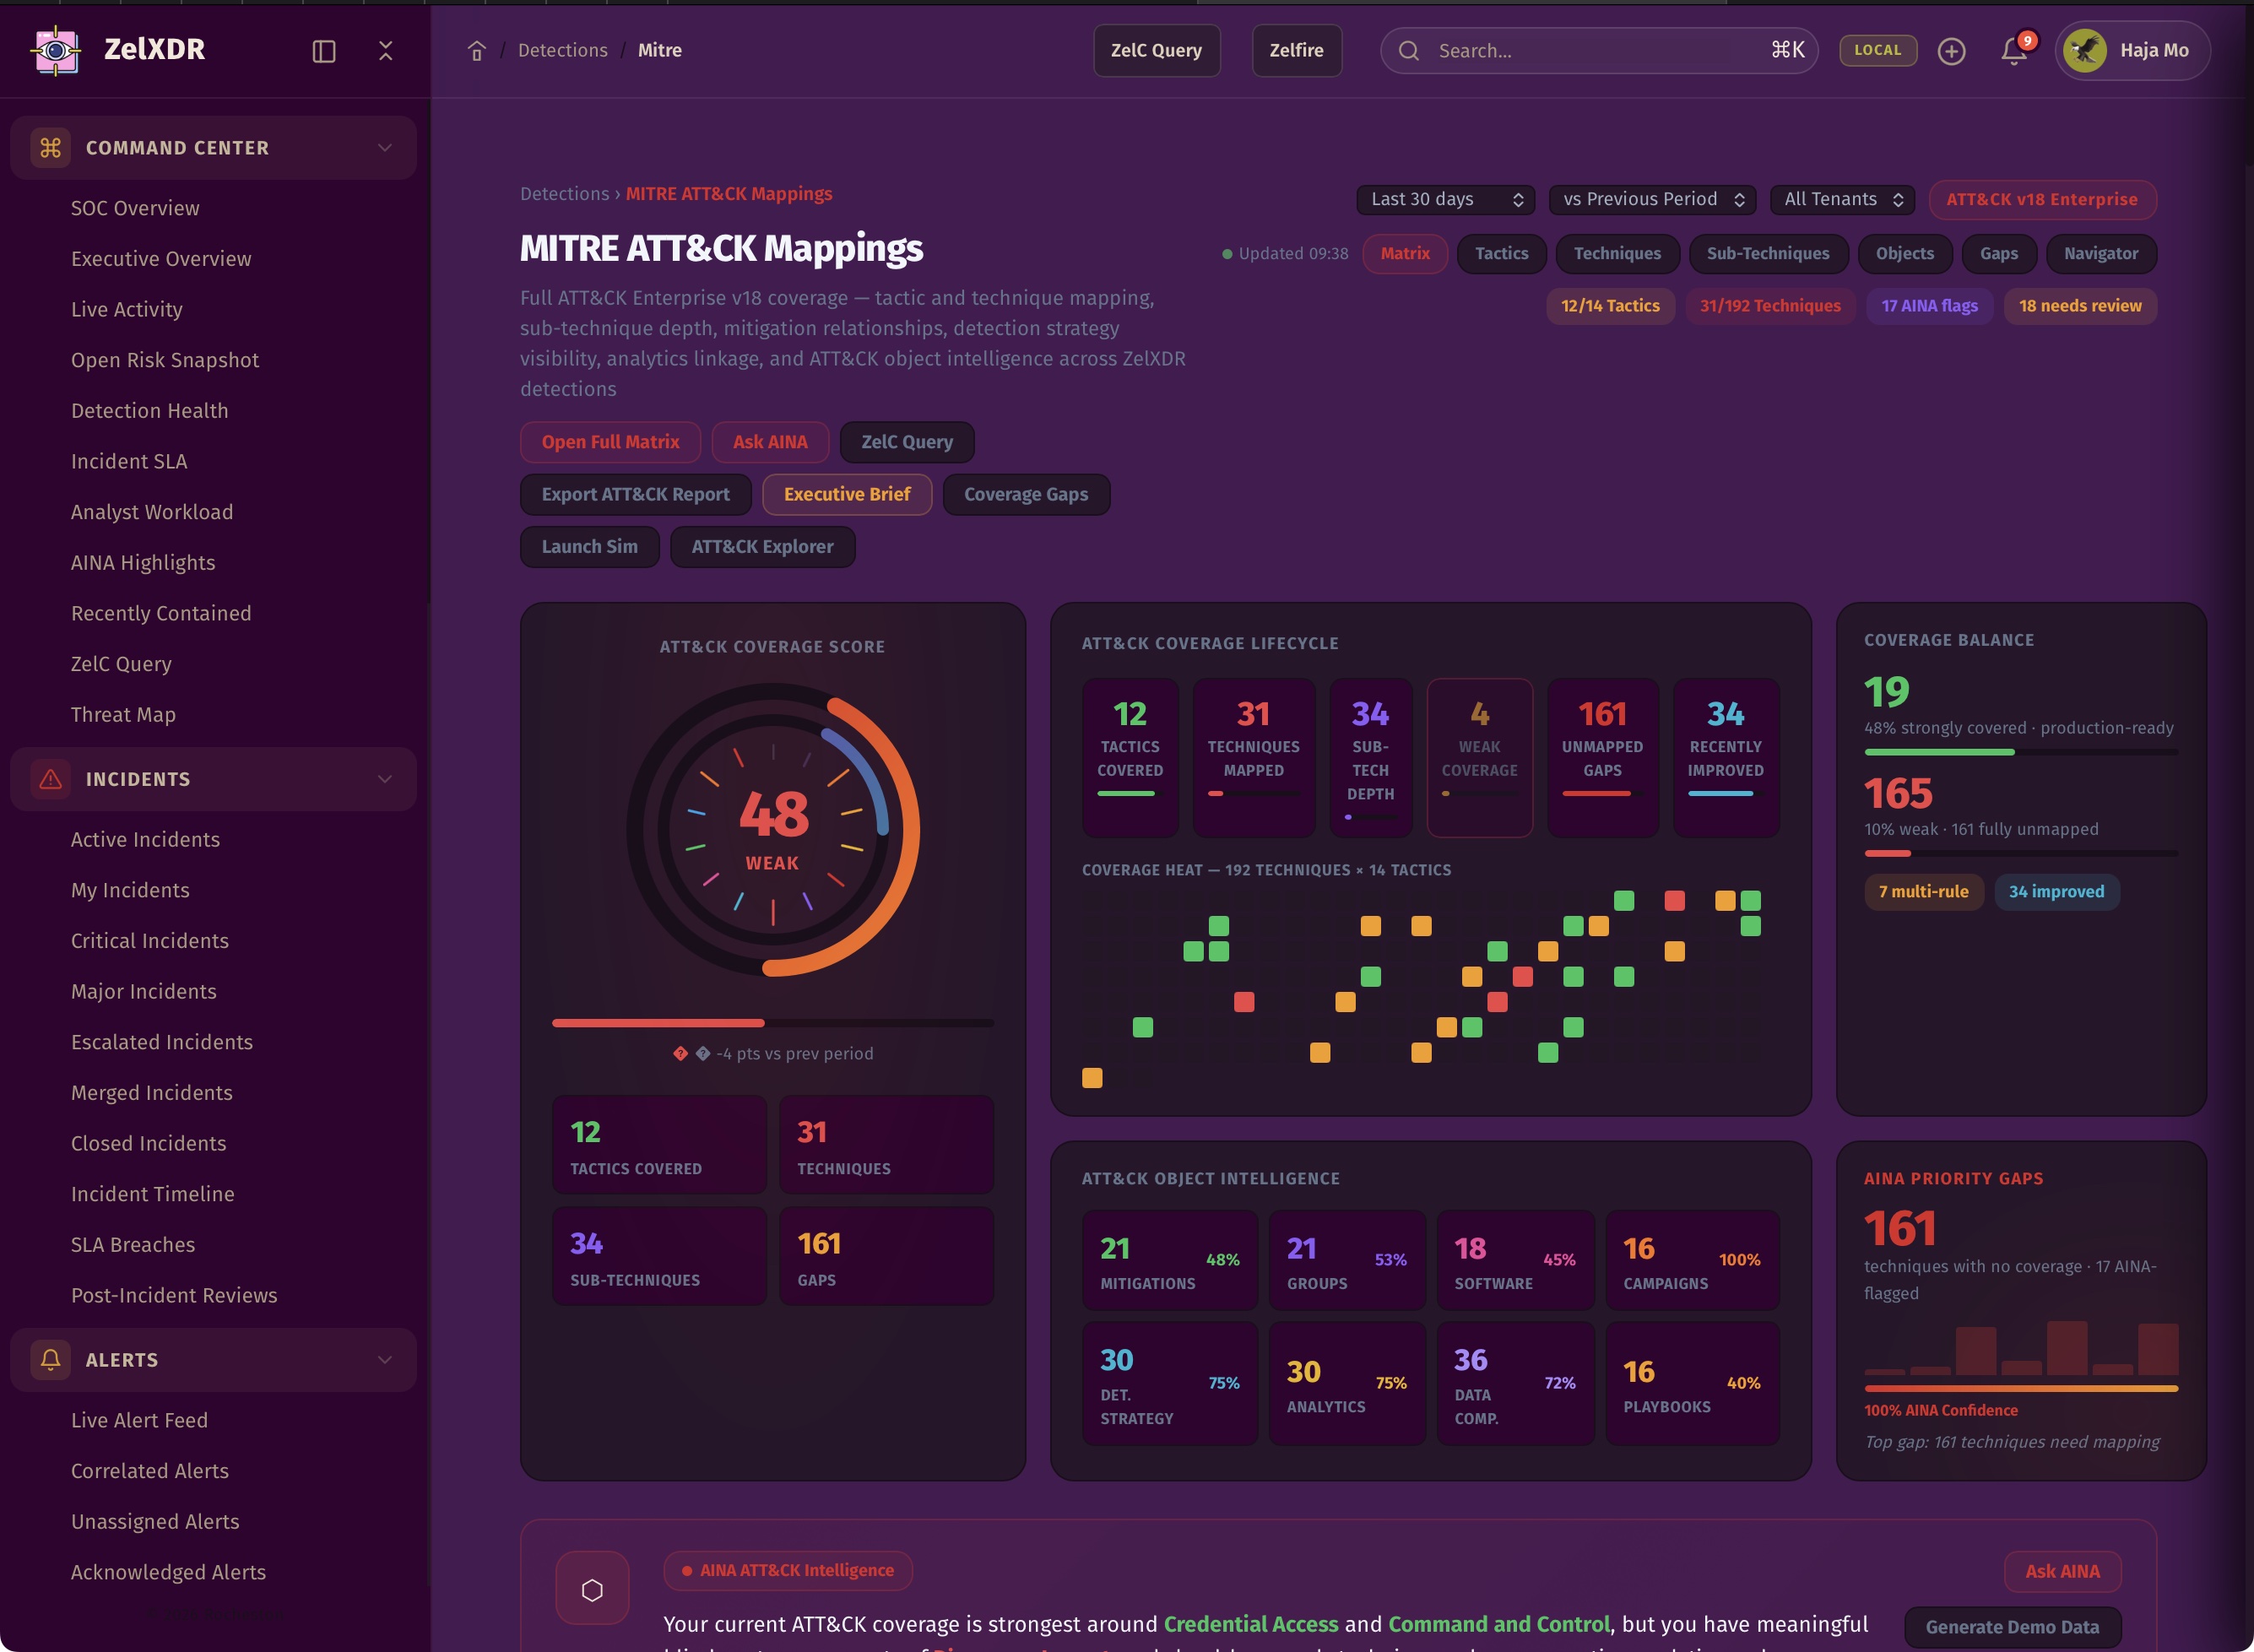
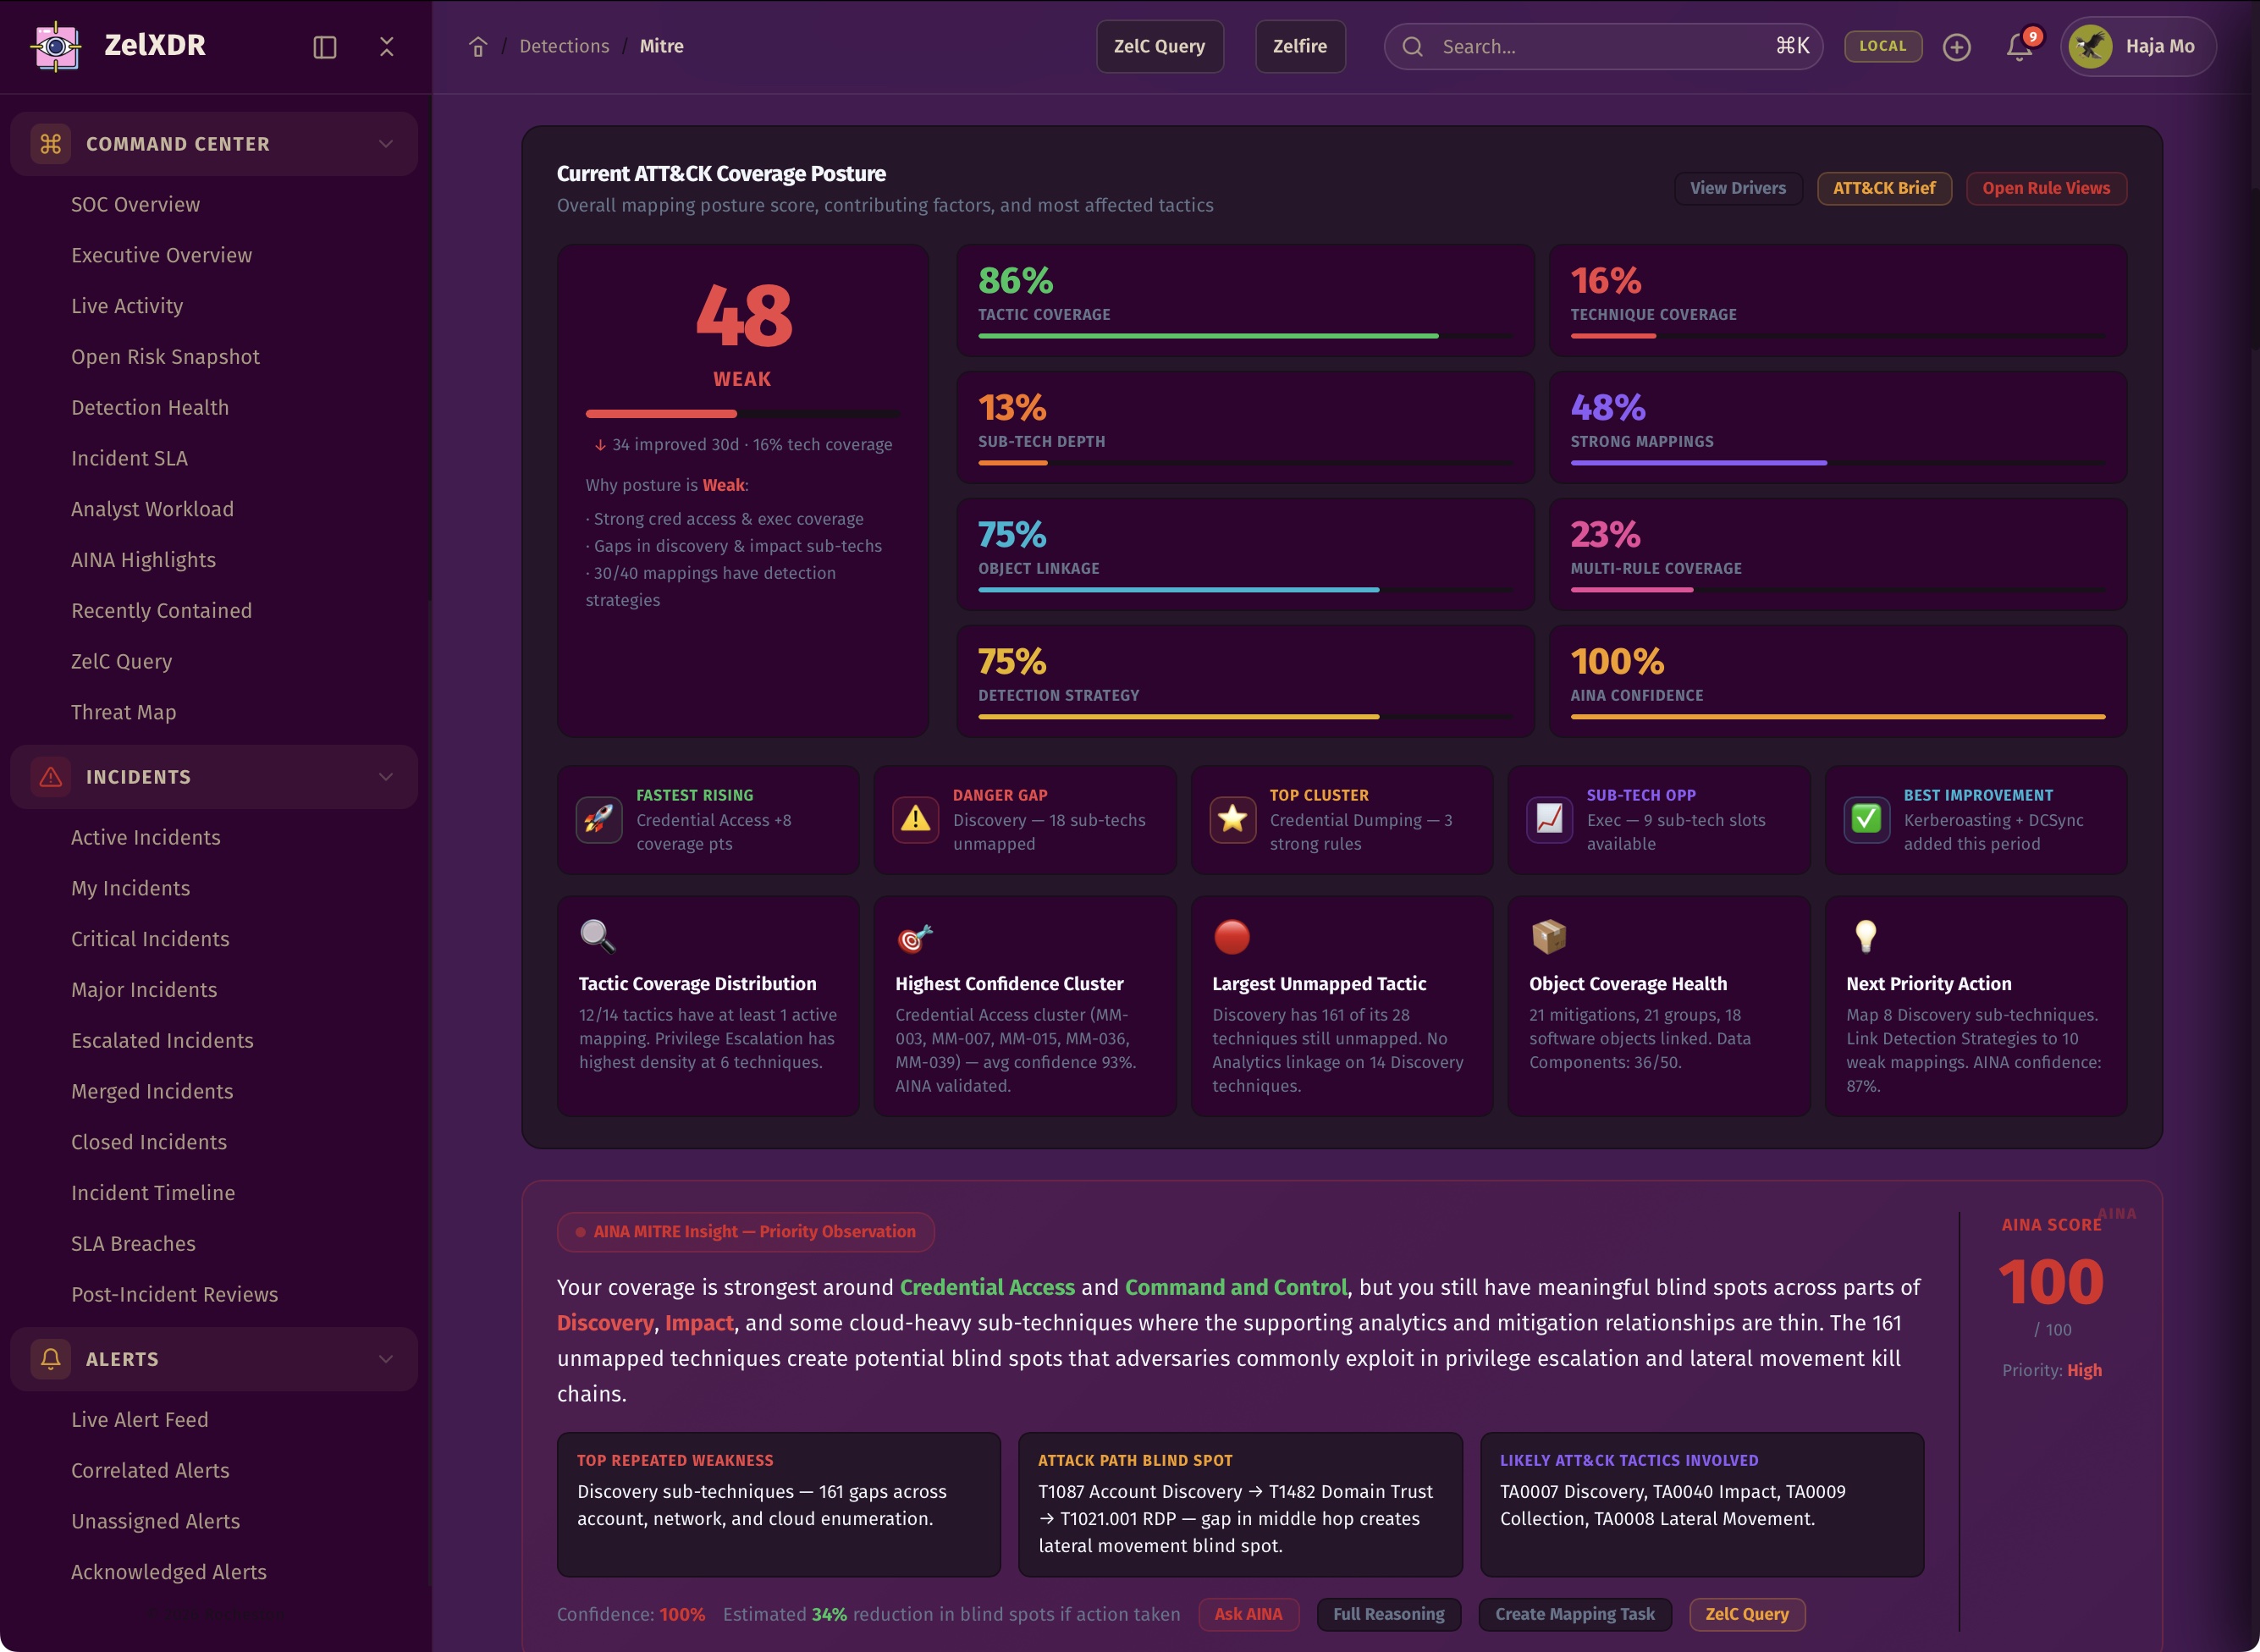
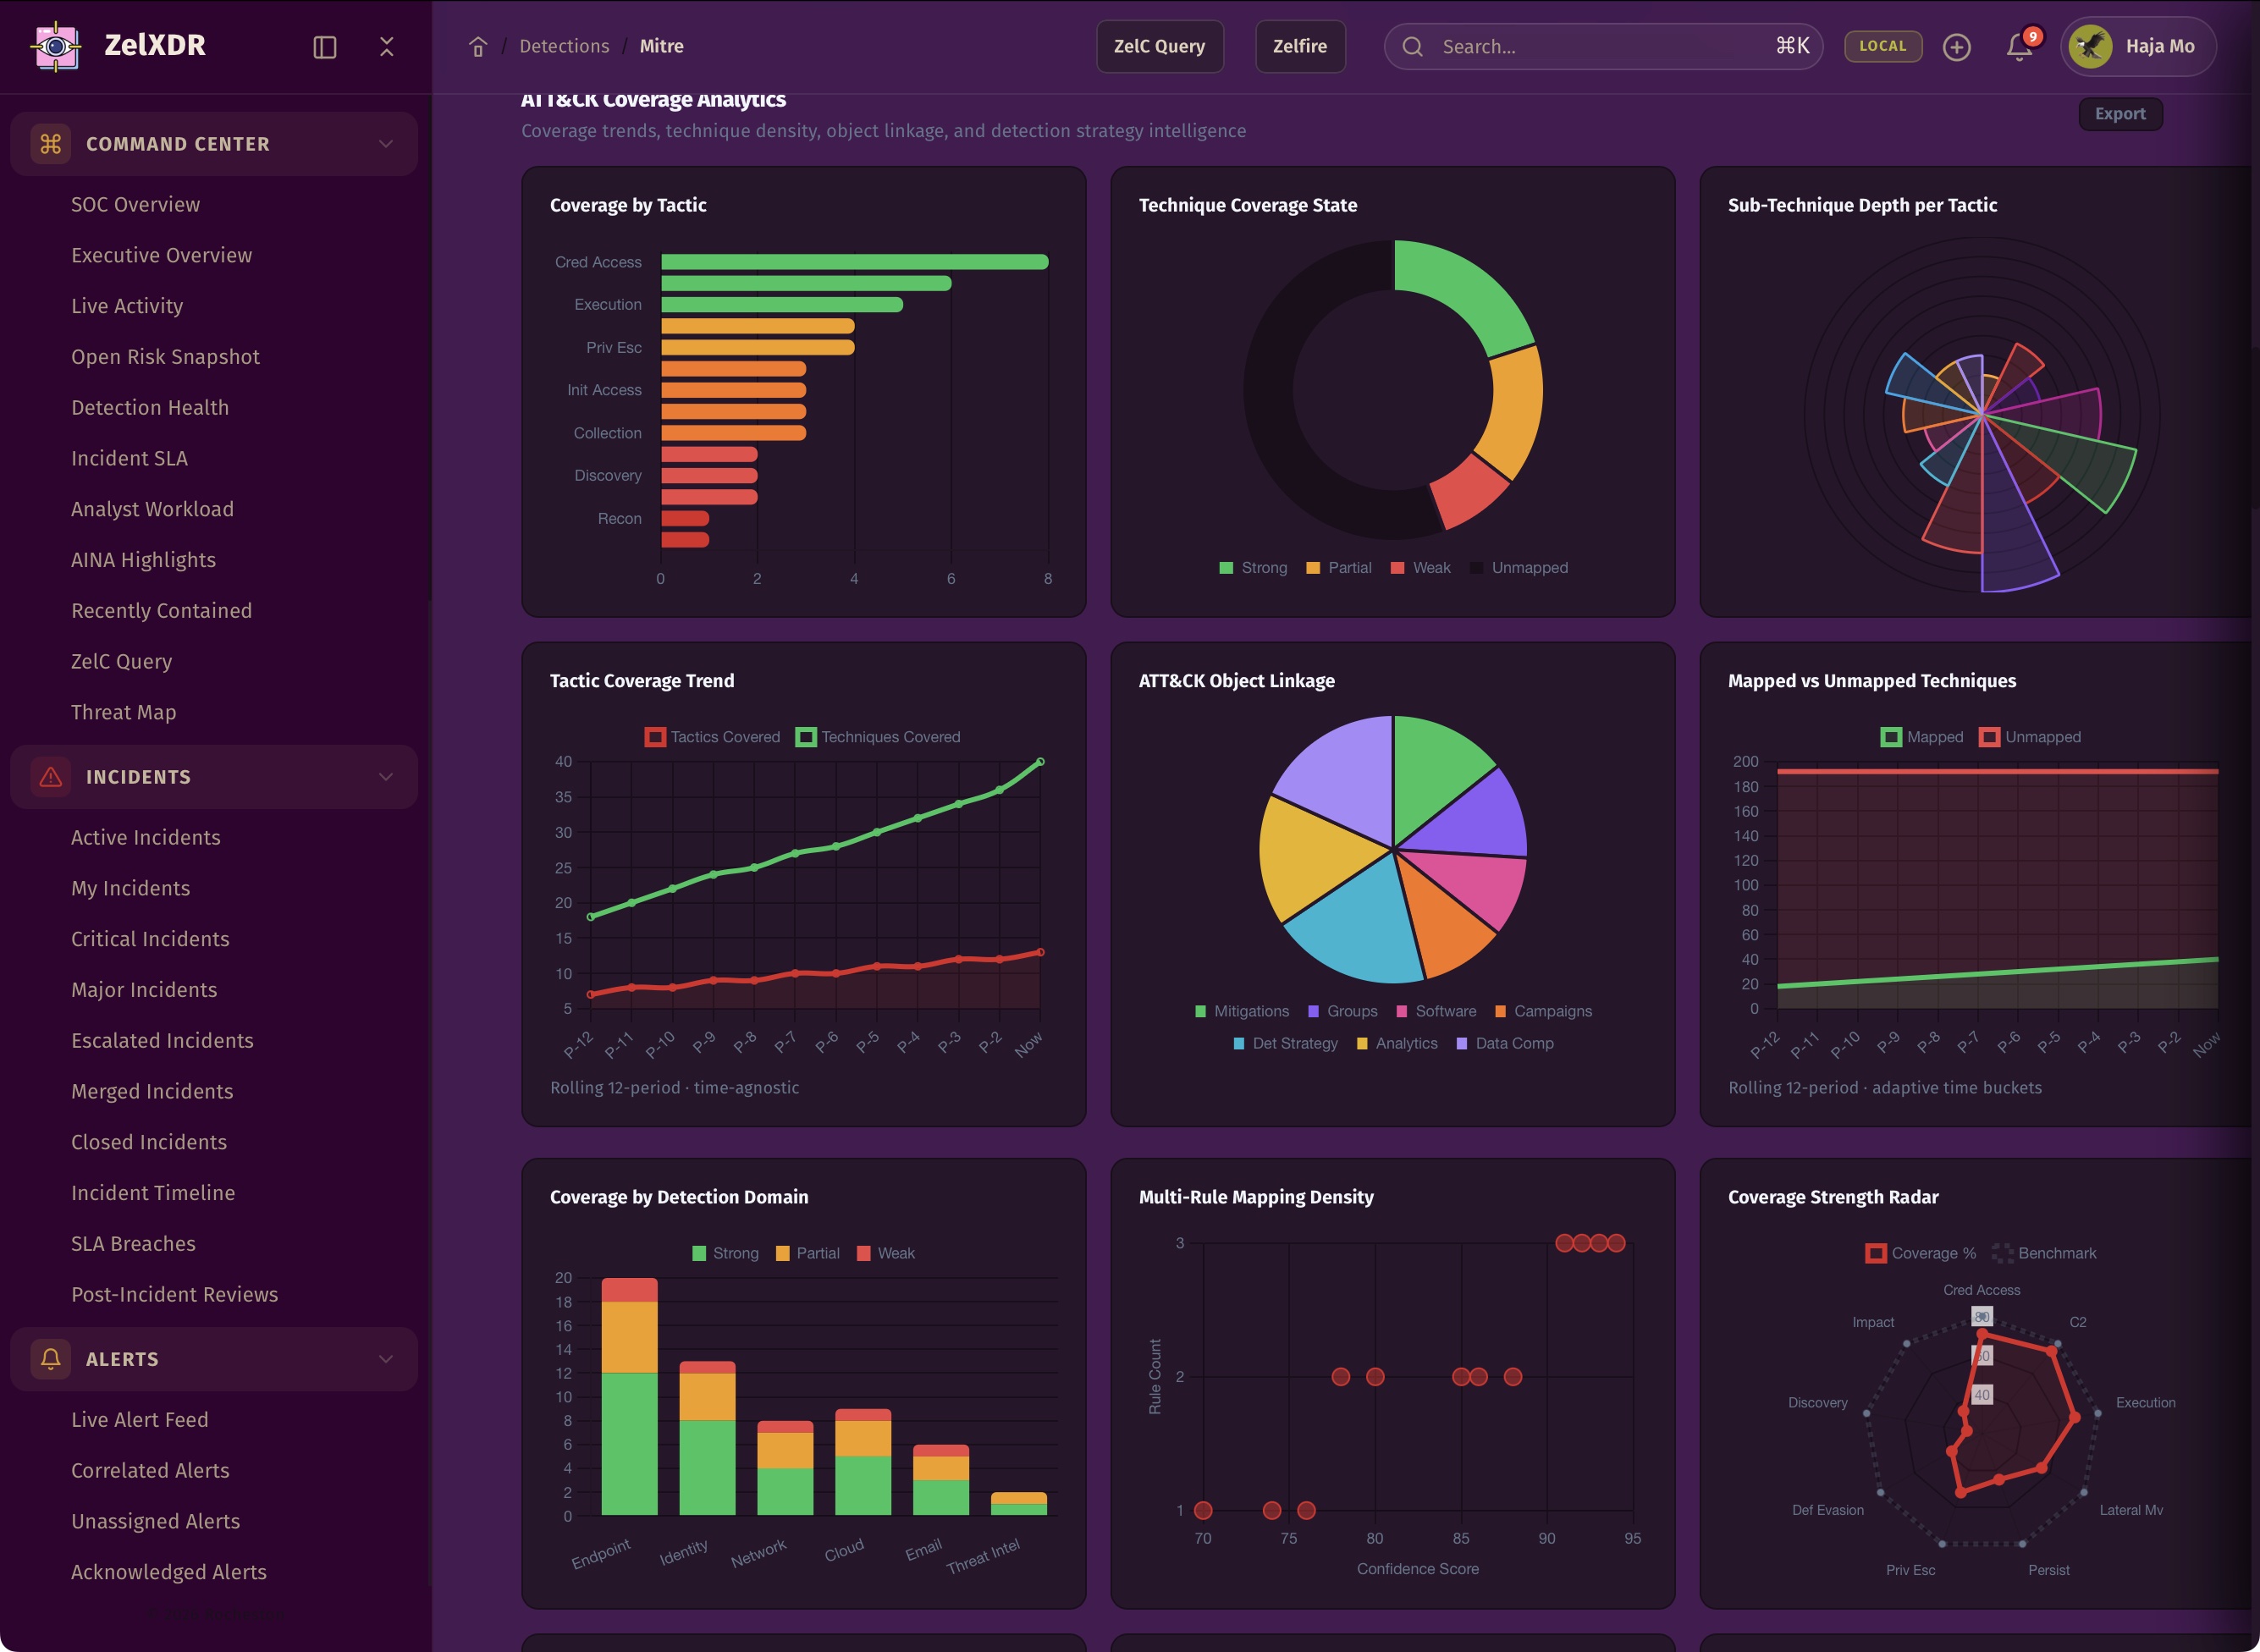
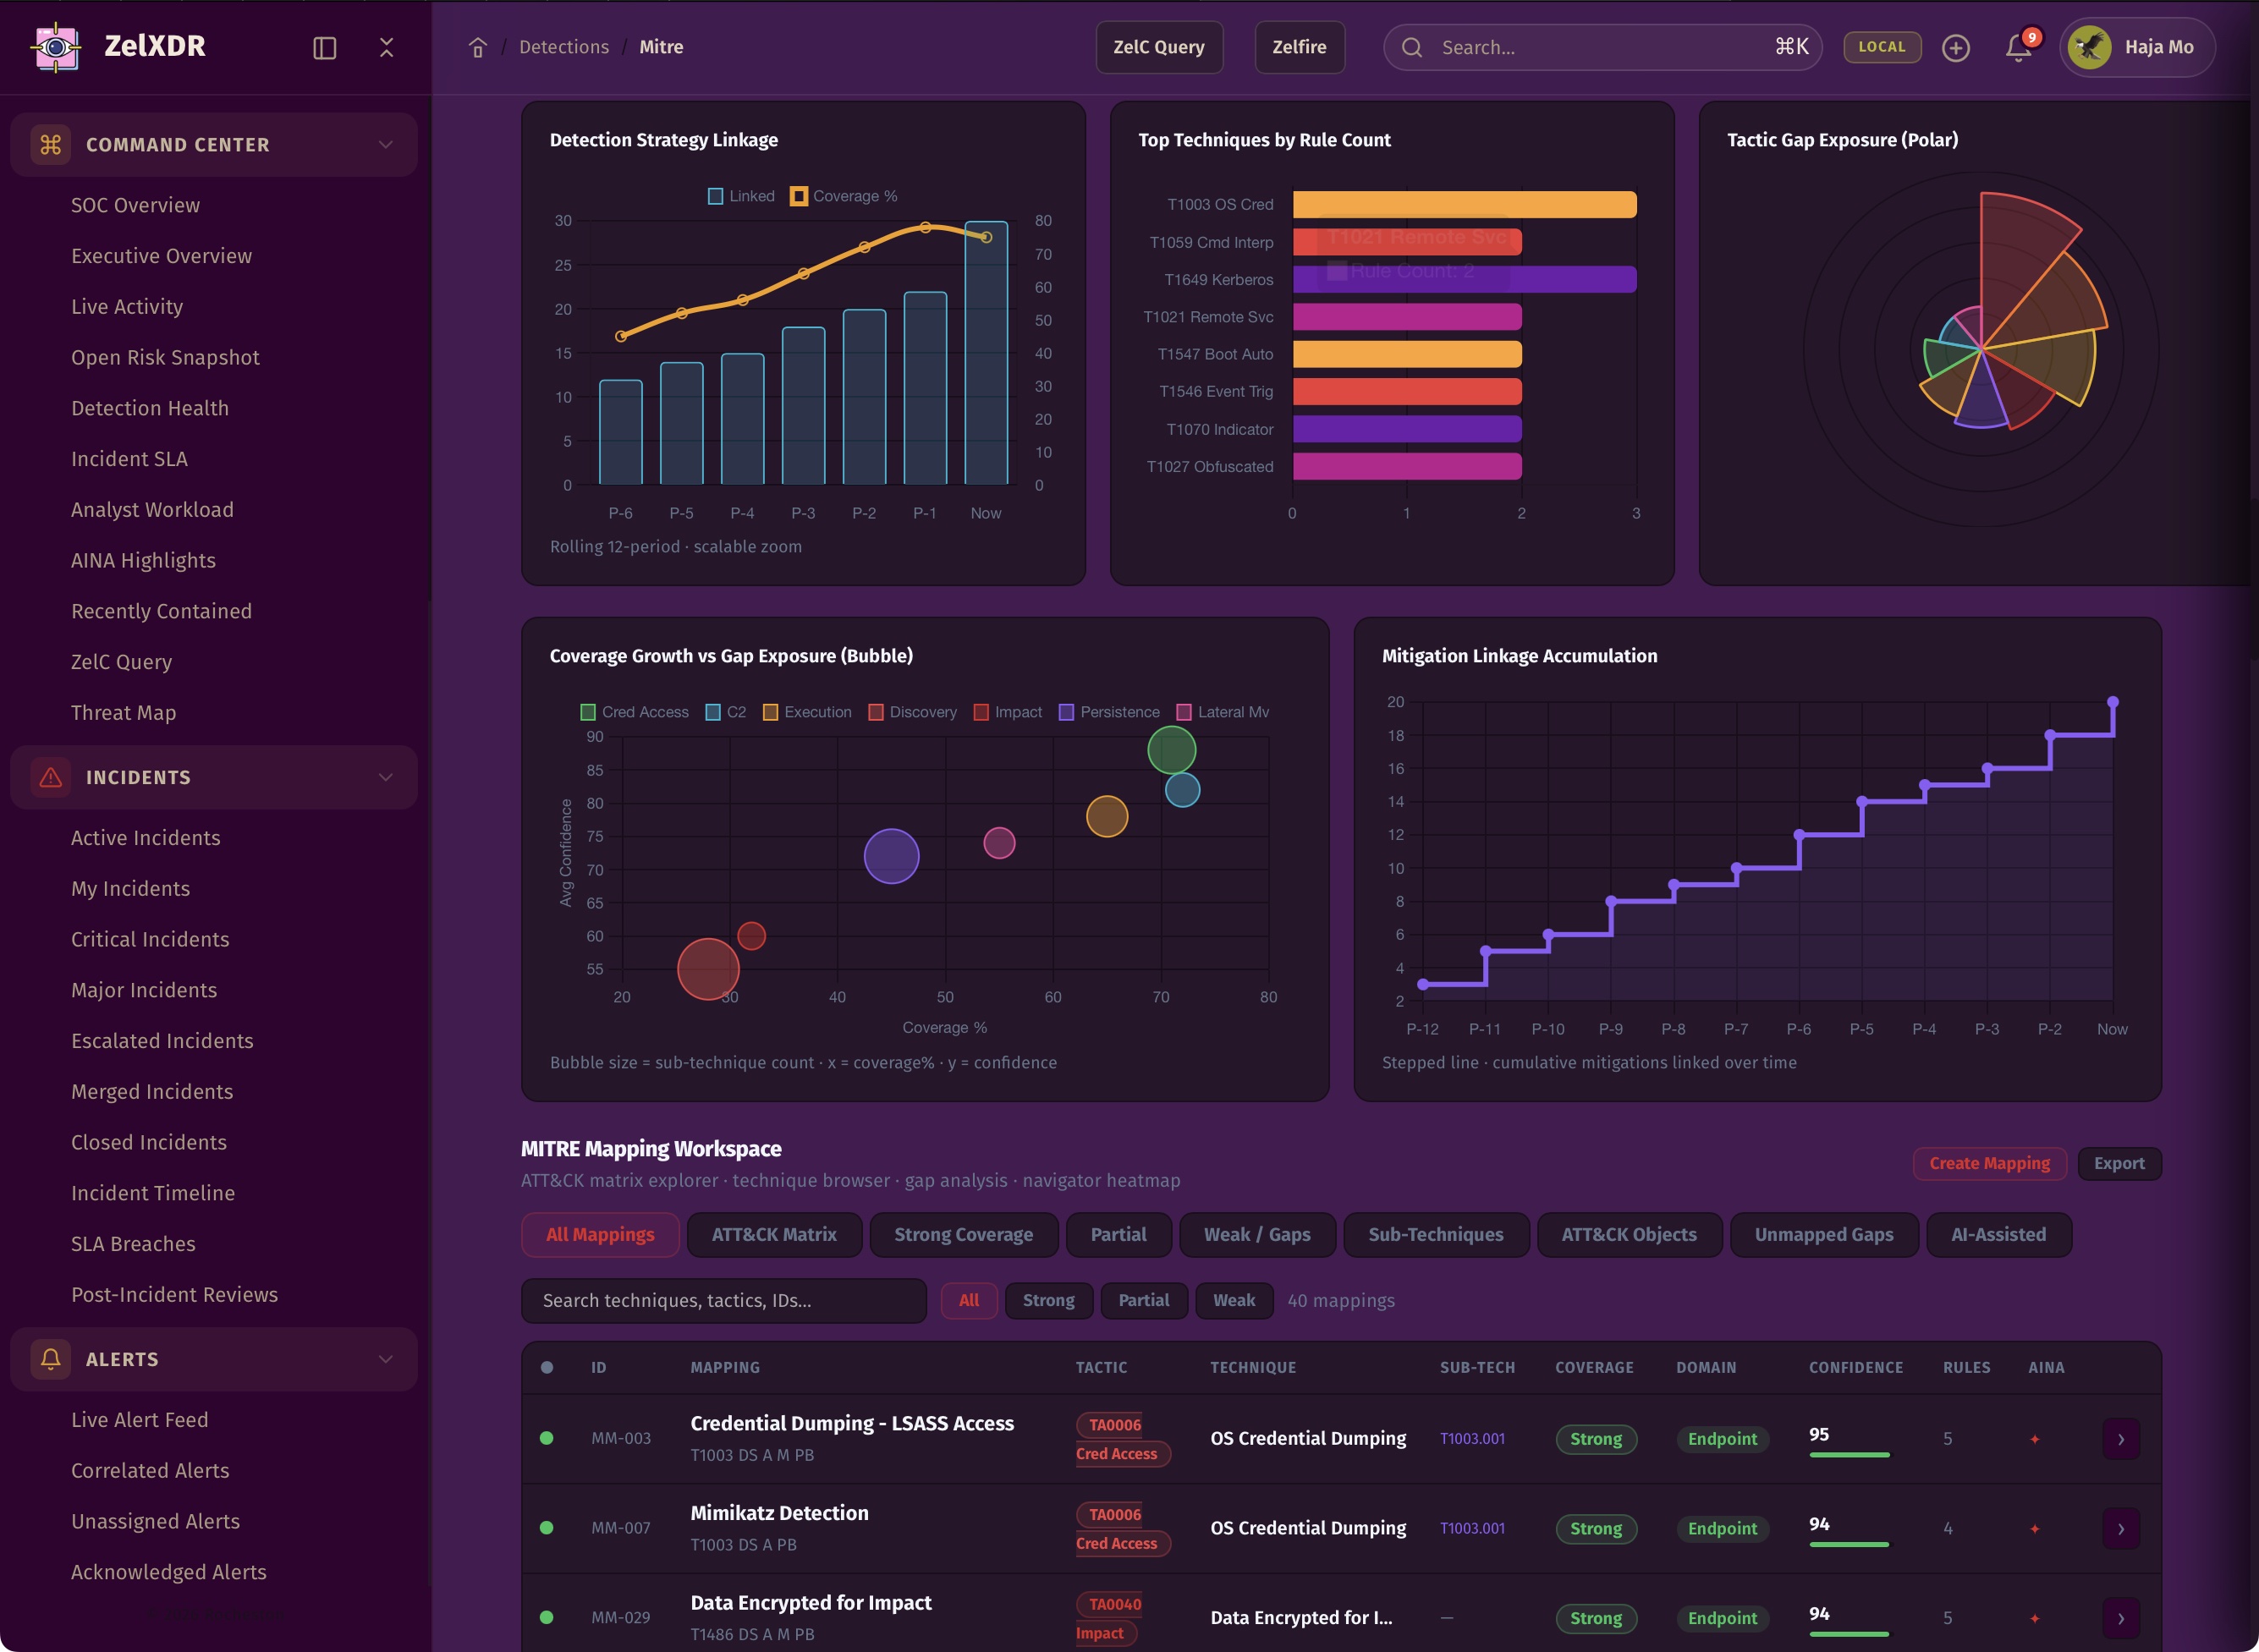
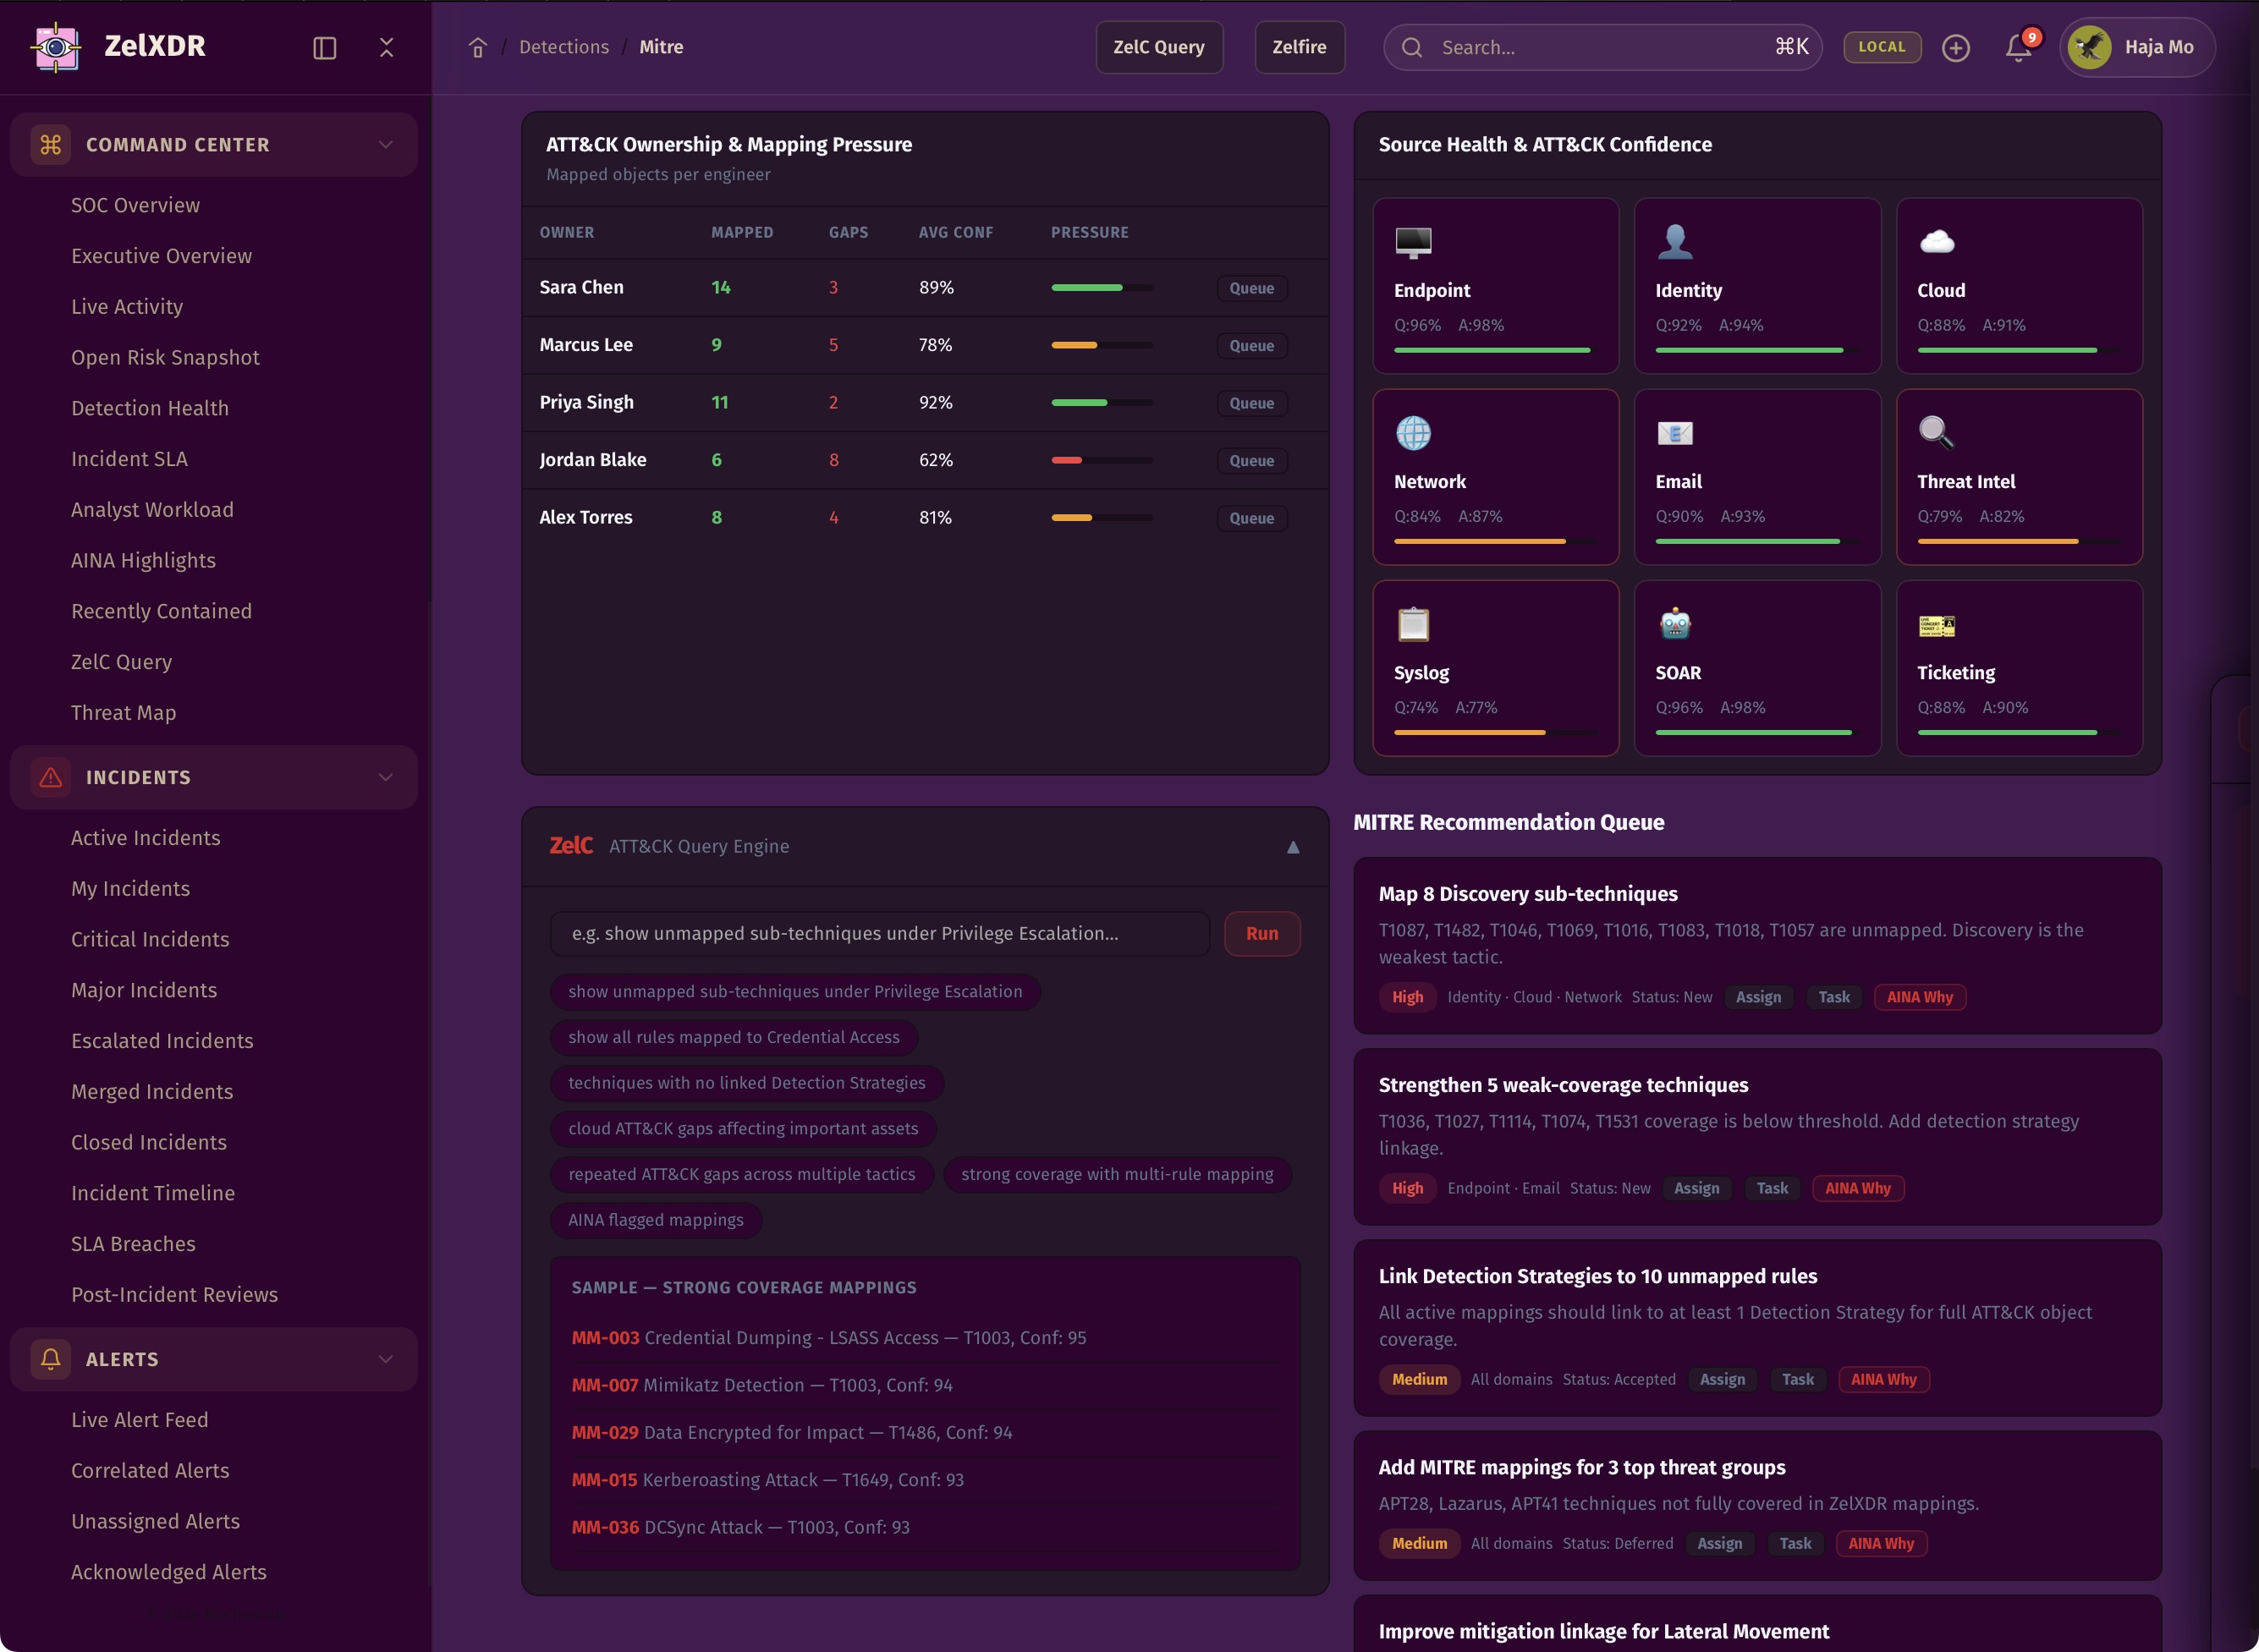
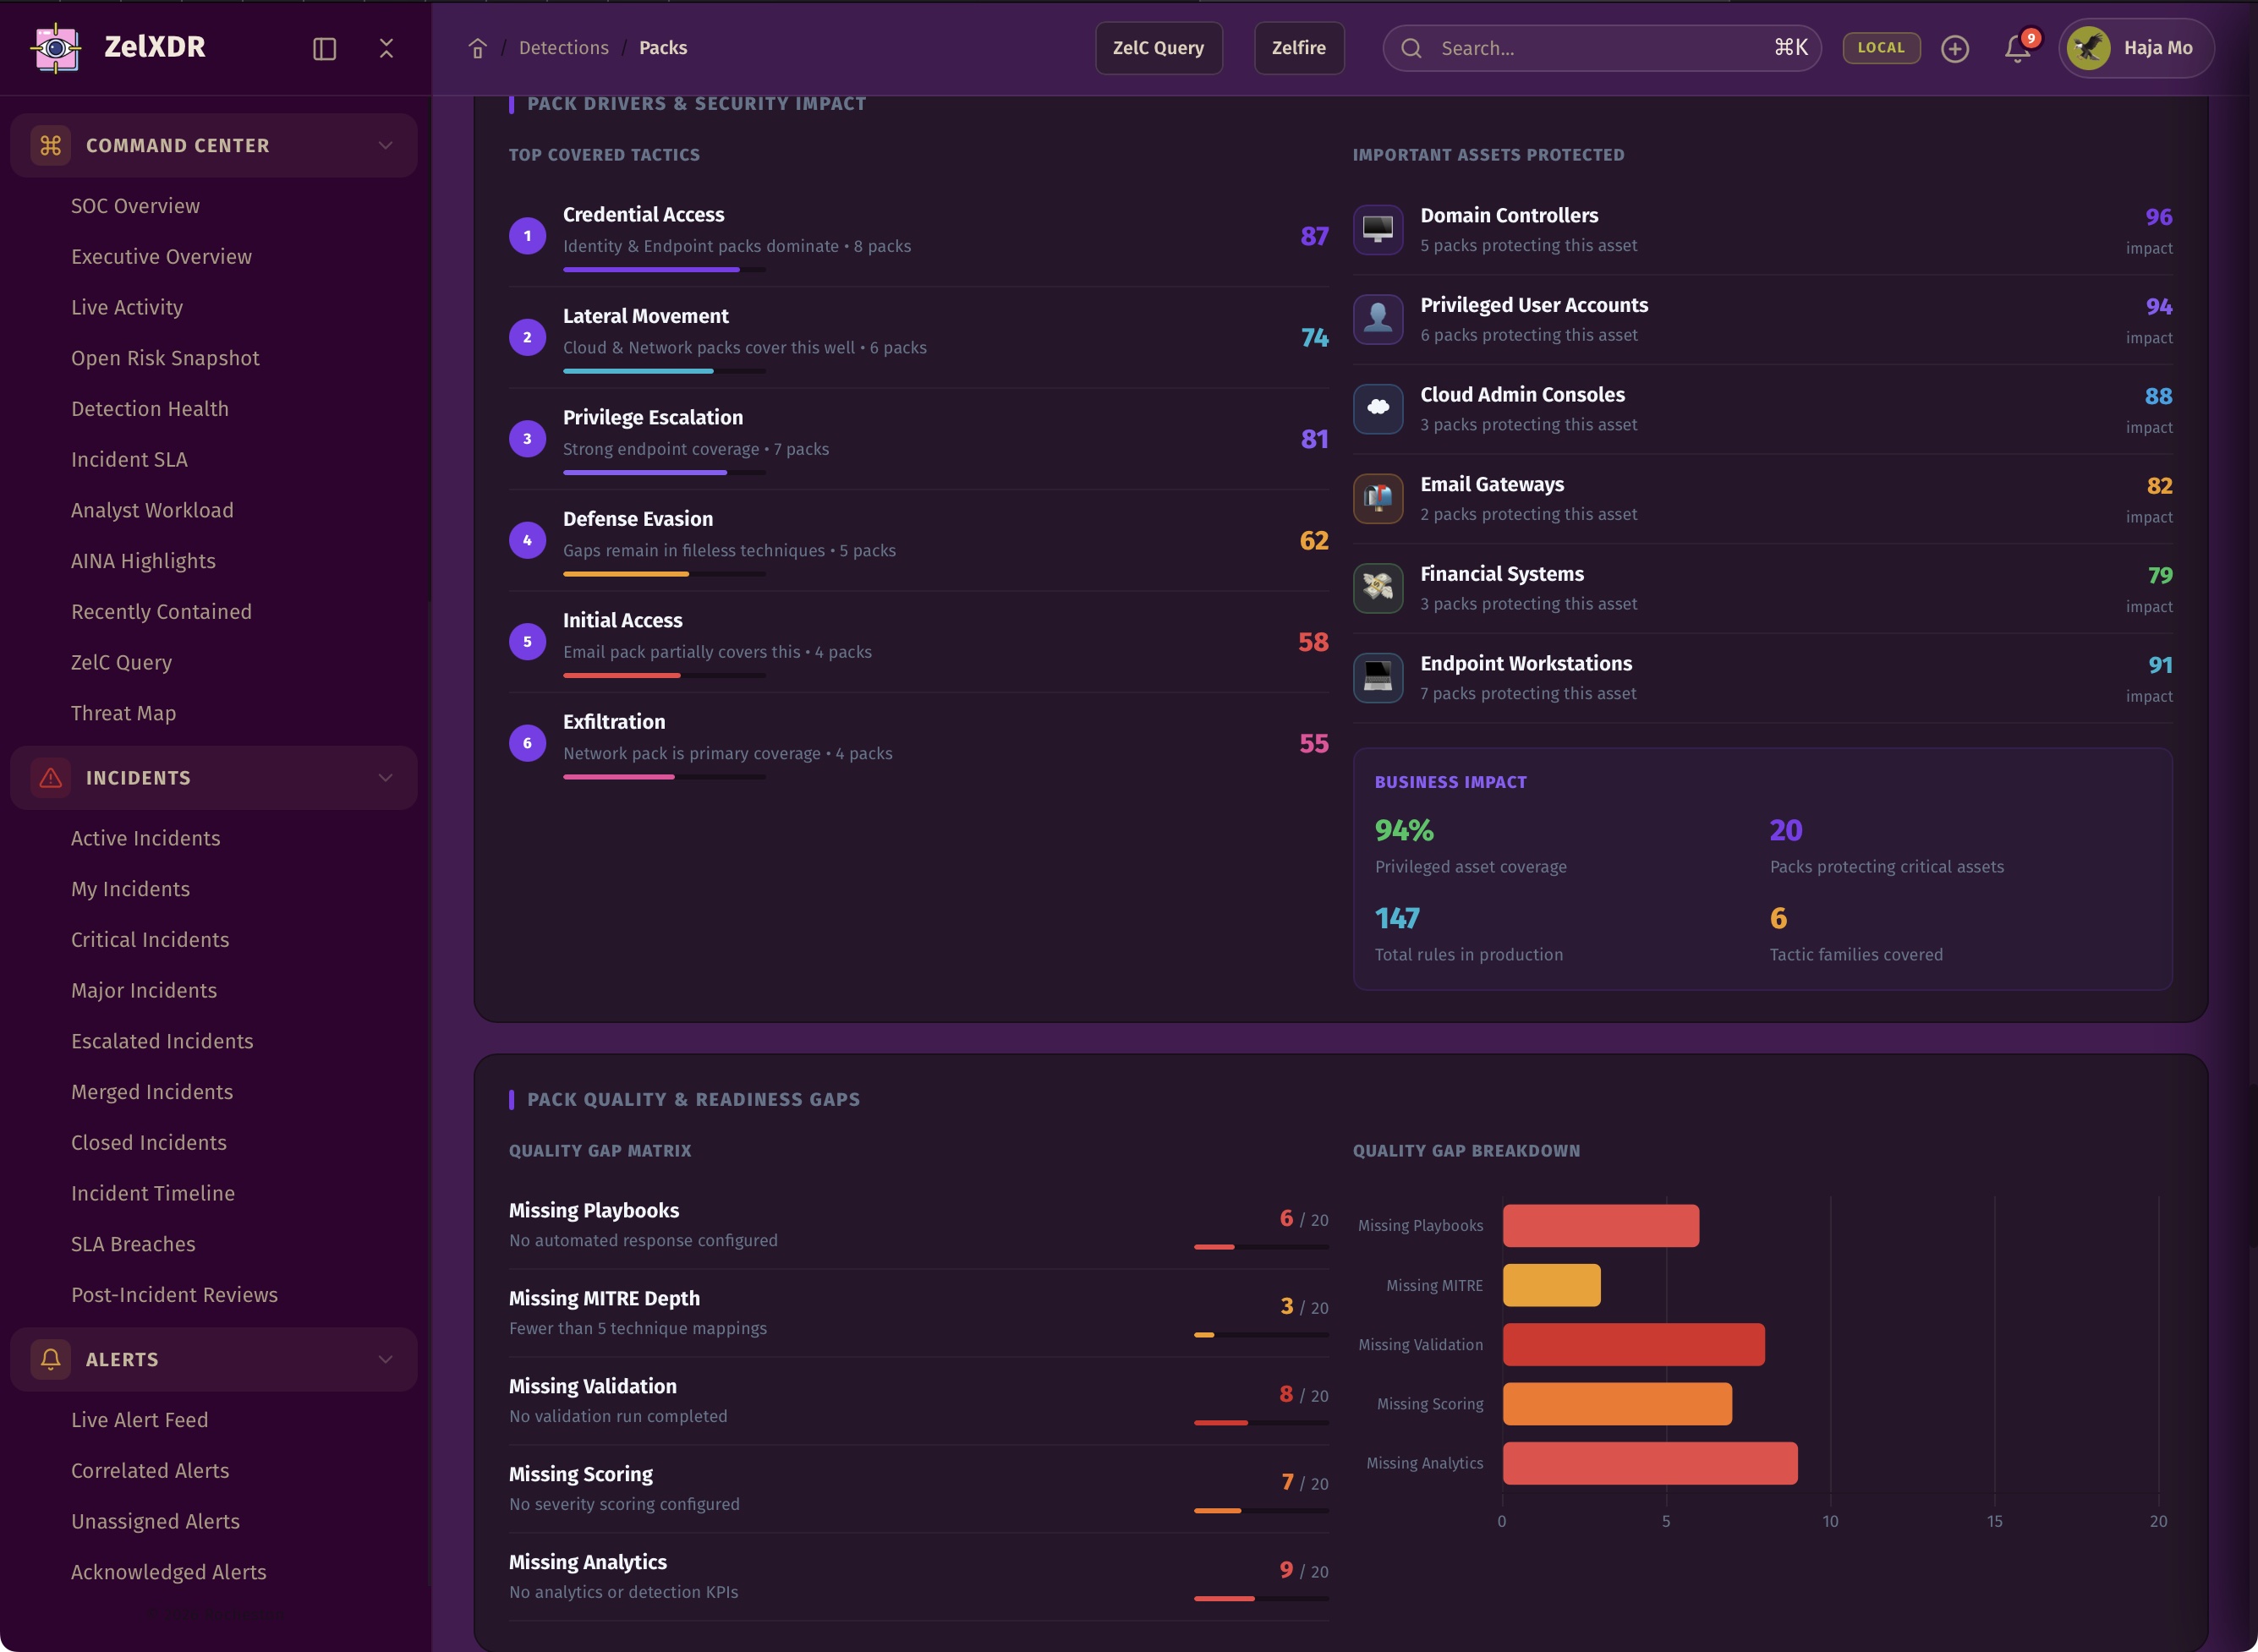
ZelXDR maps platform logic and findings to ATT&CK tactics, techniques, and sub-techniques so coverage can be measured, improved, and explained in a meaningful way.
Coverage becomes strategic when it aligns to real attacker behavior.
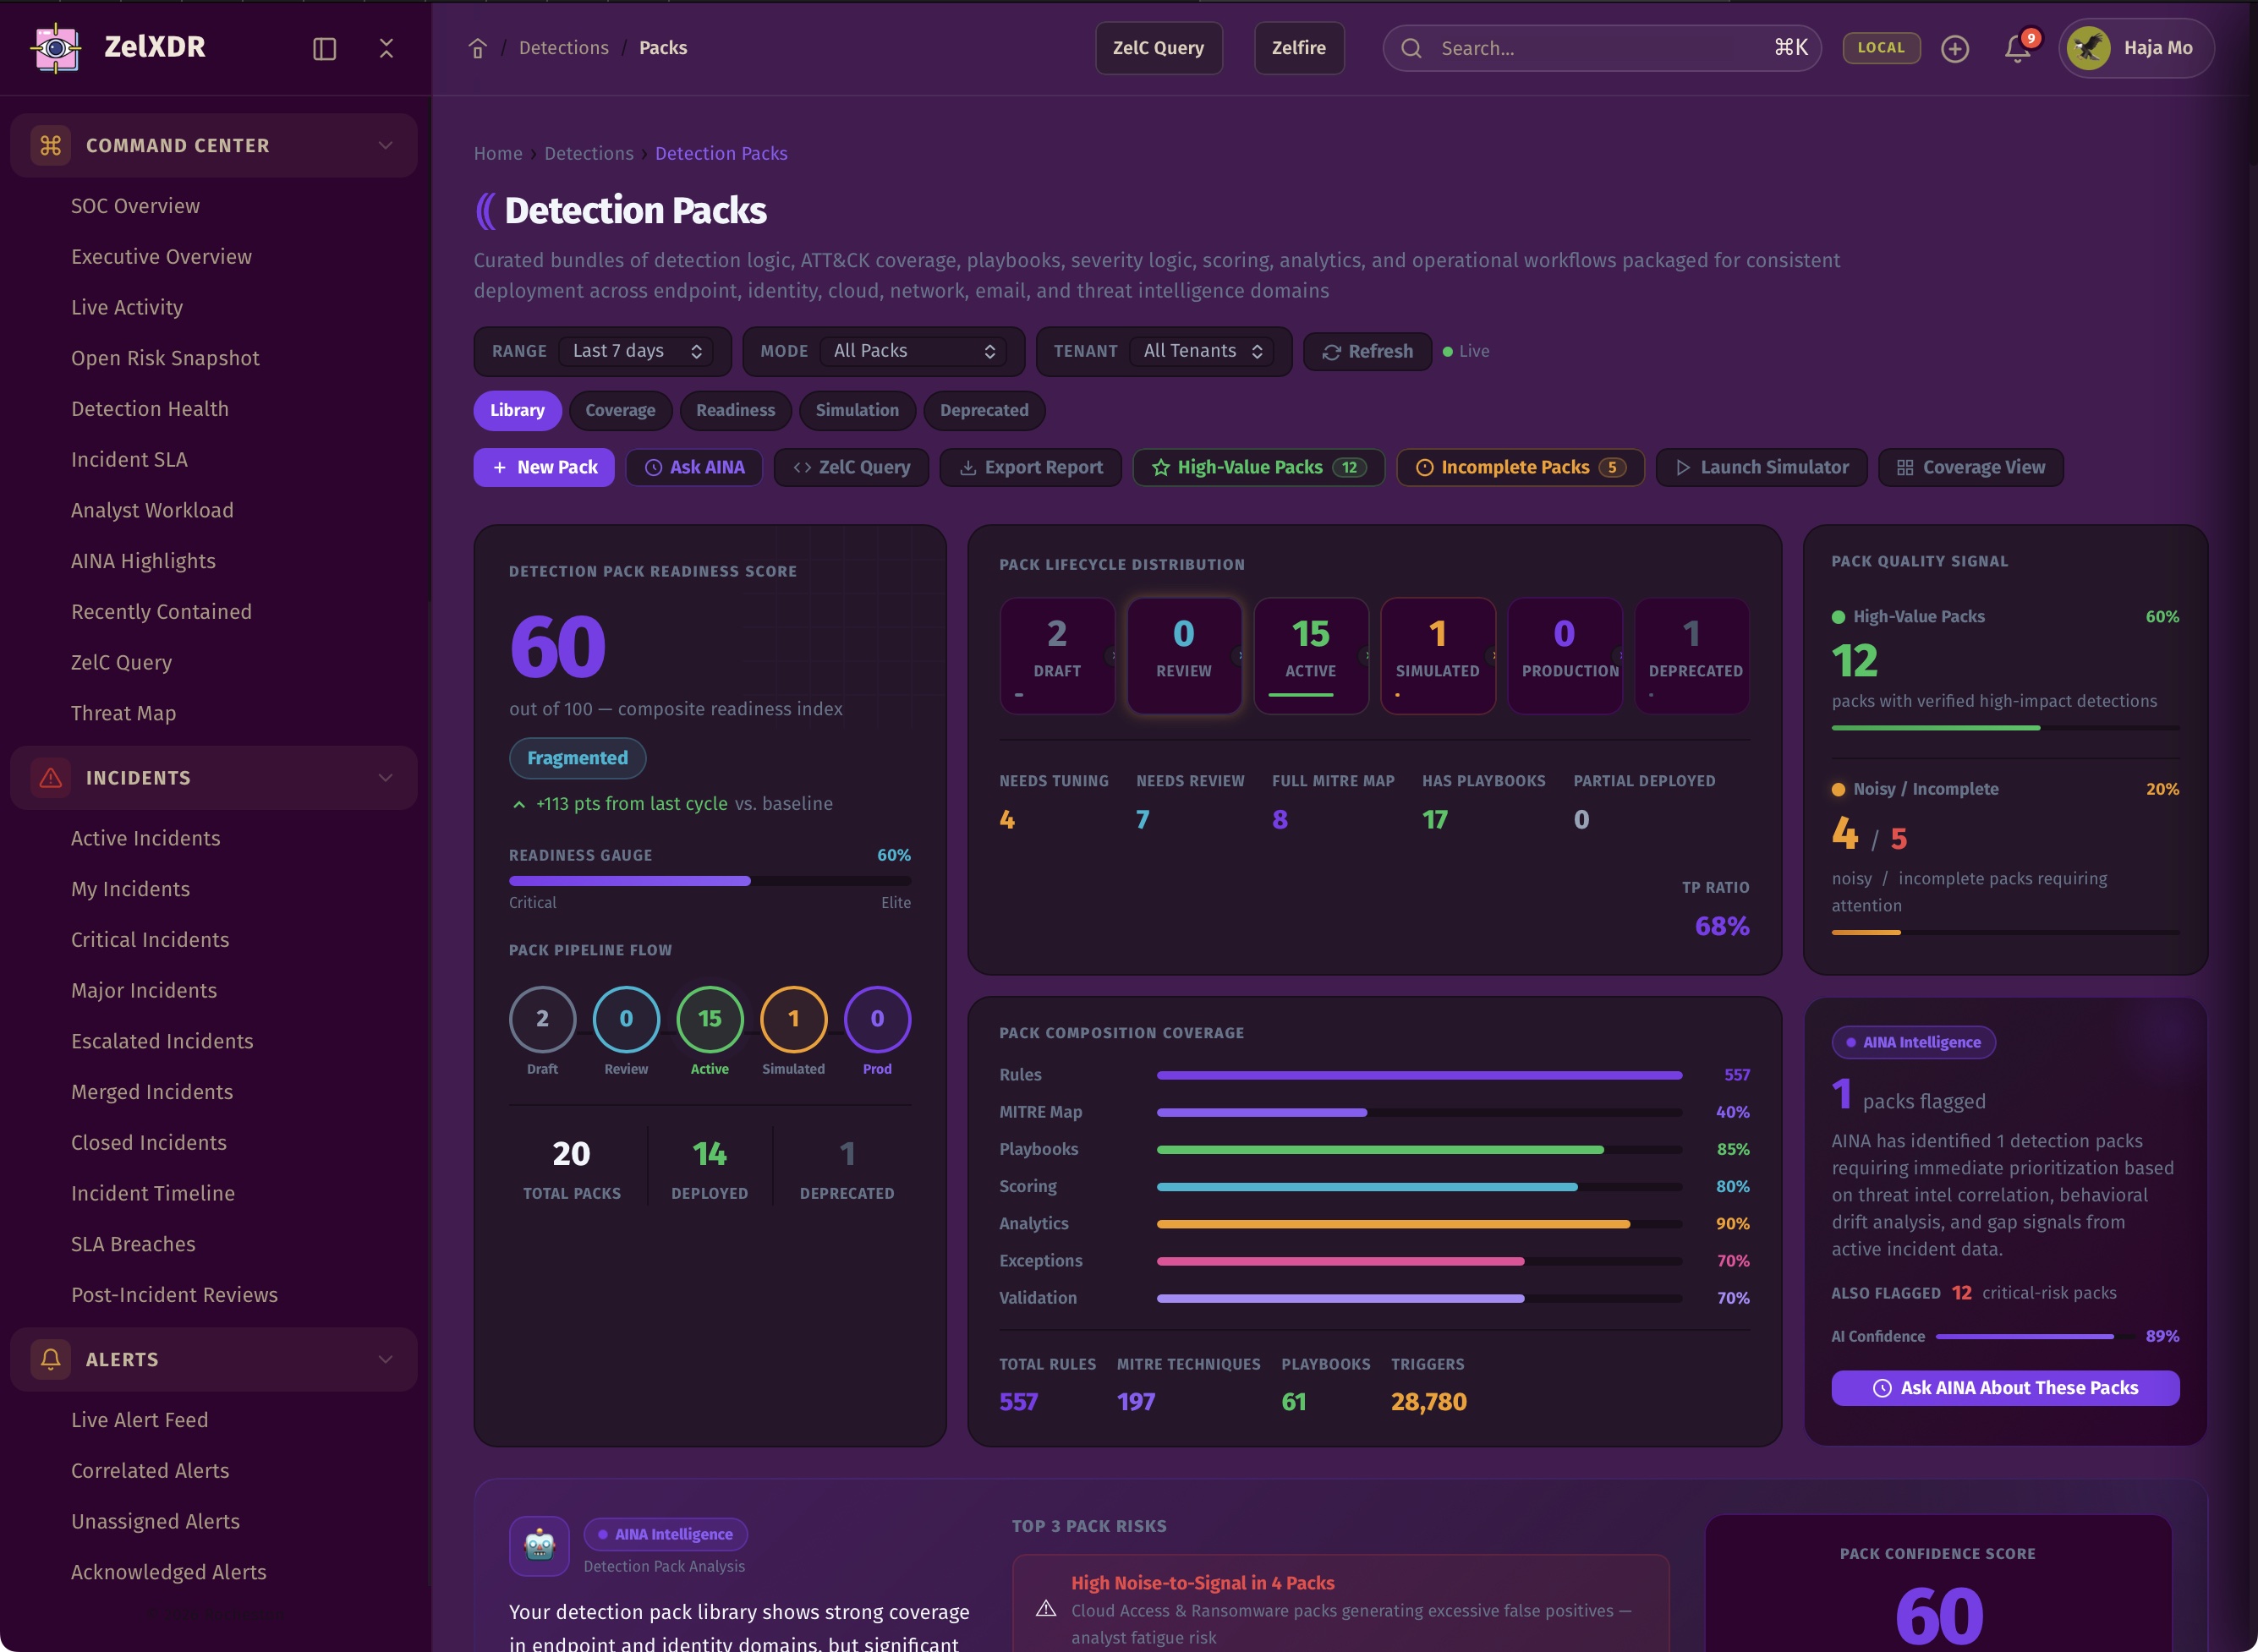
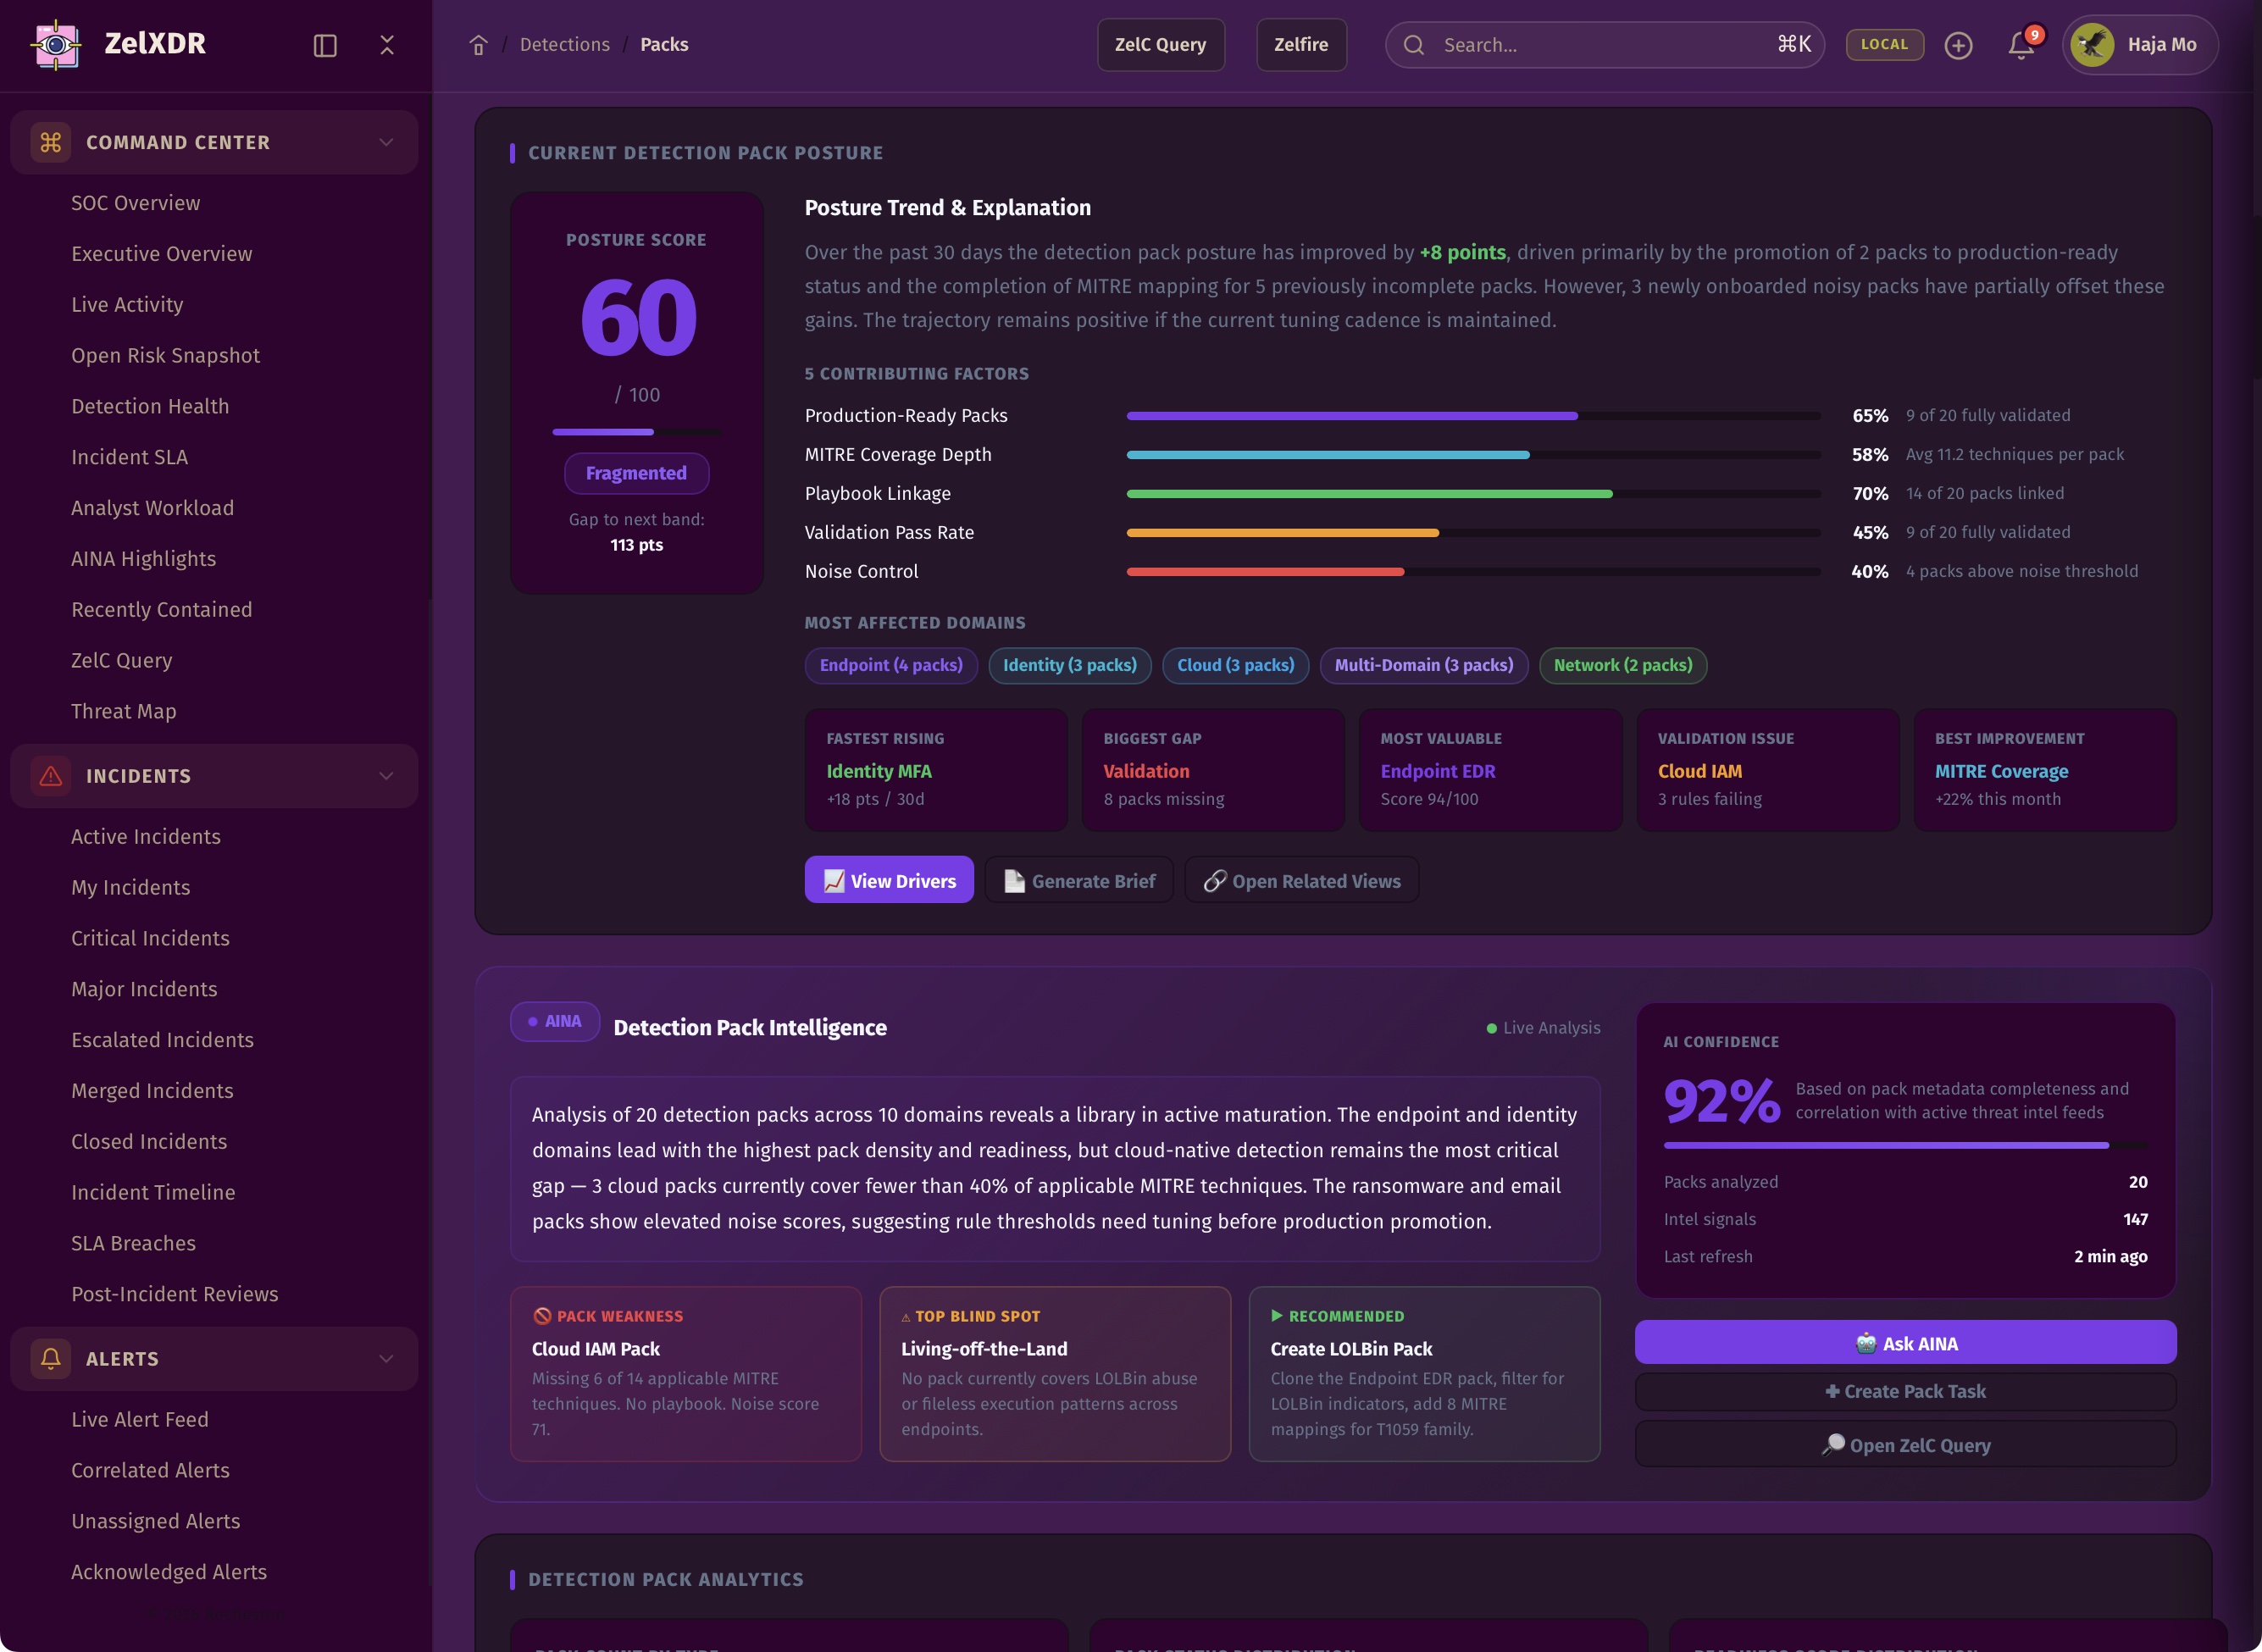
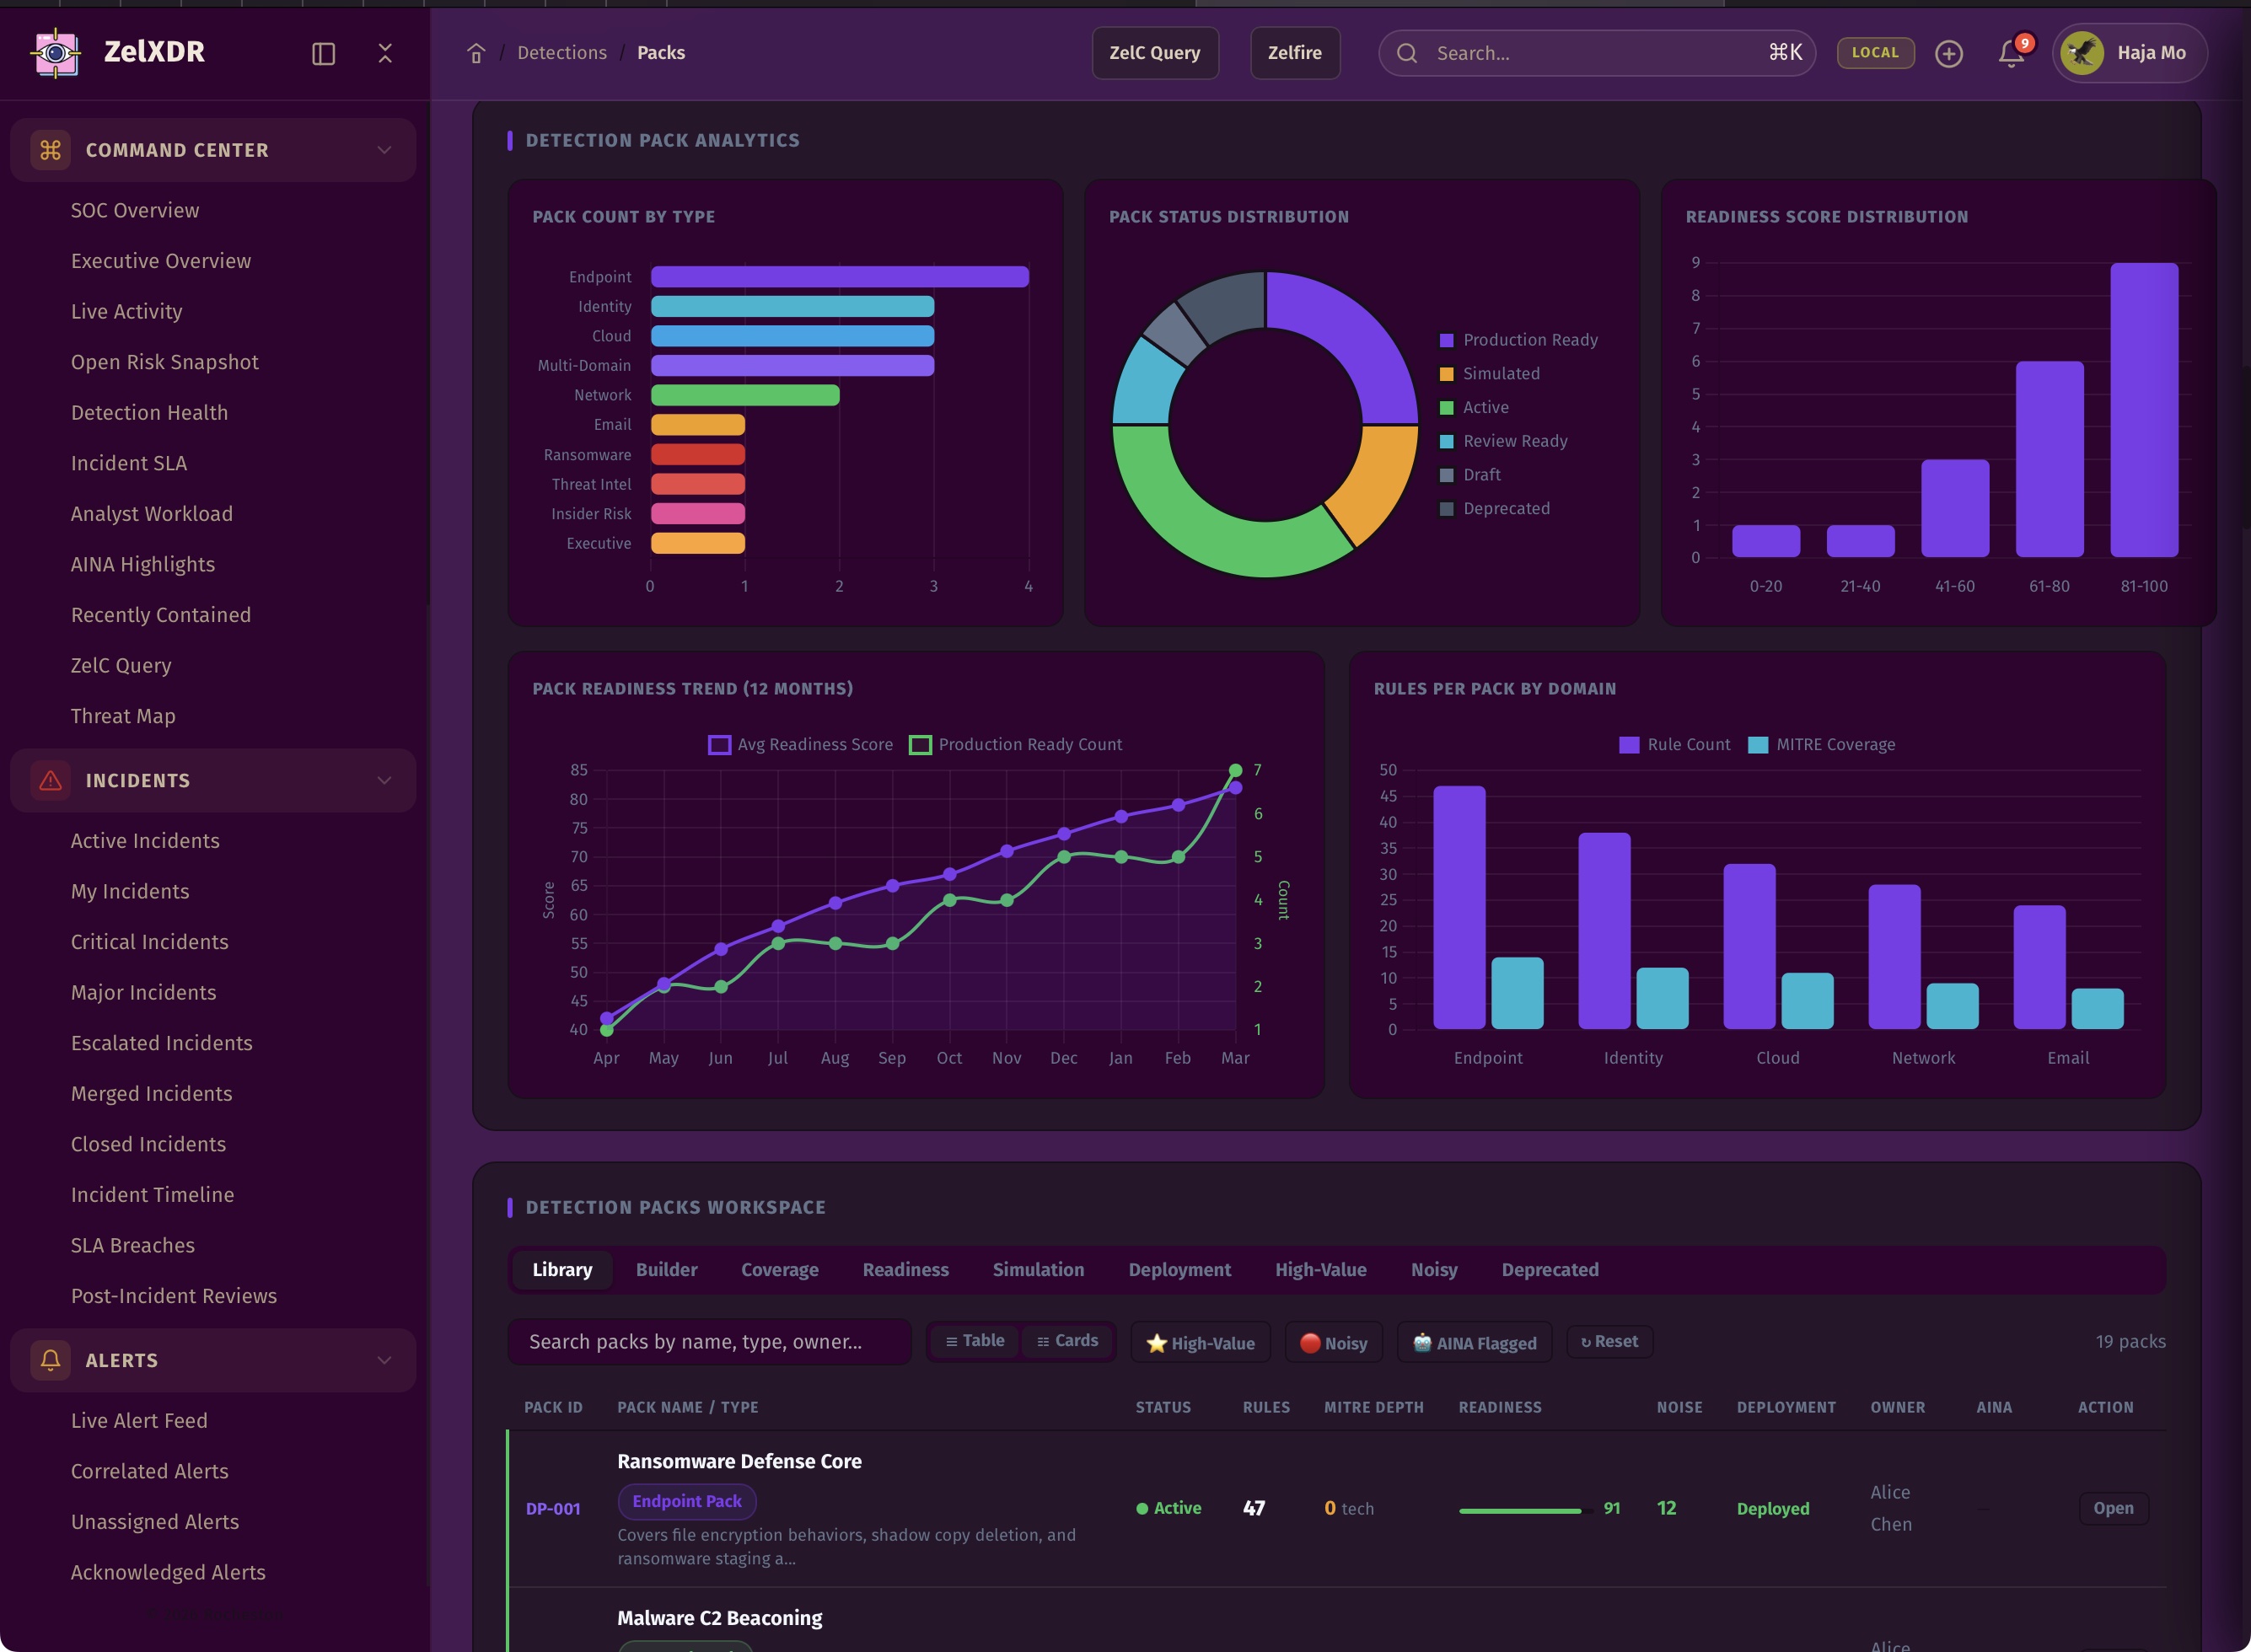
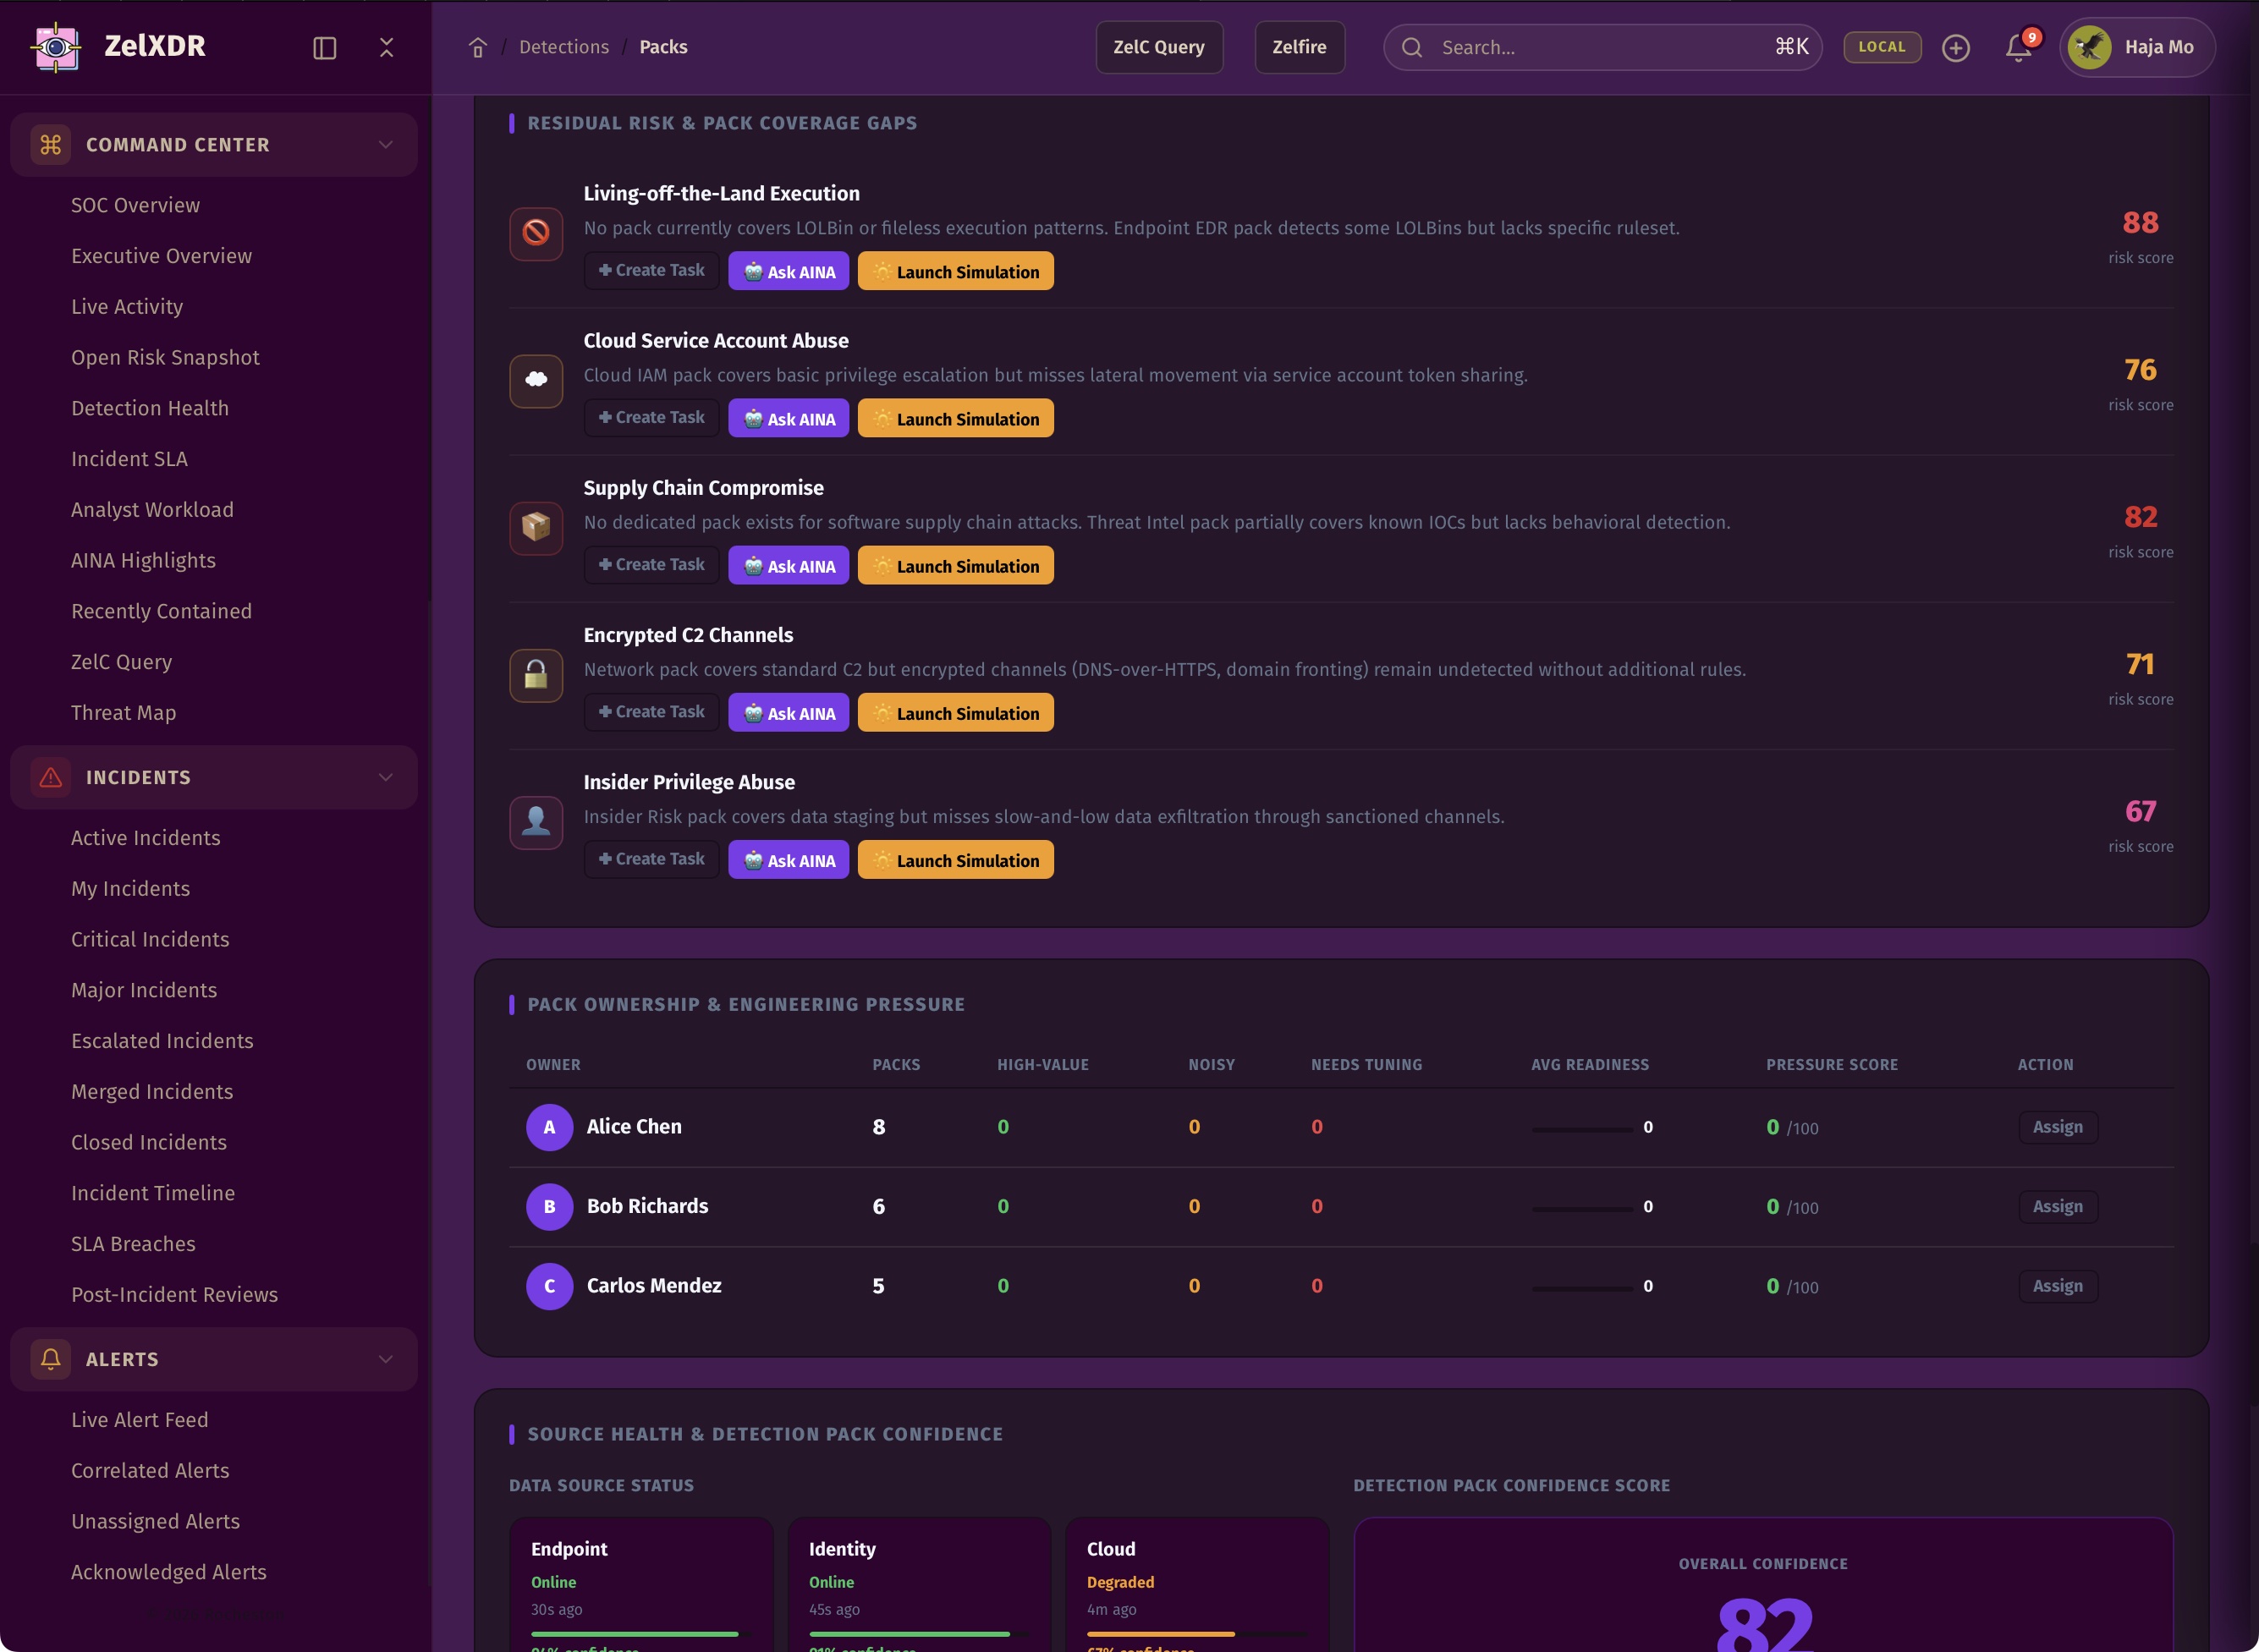
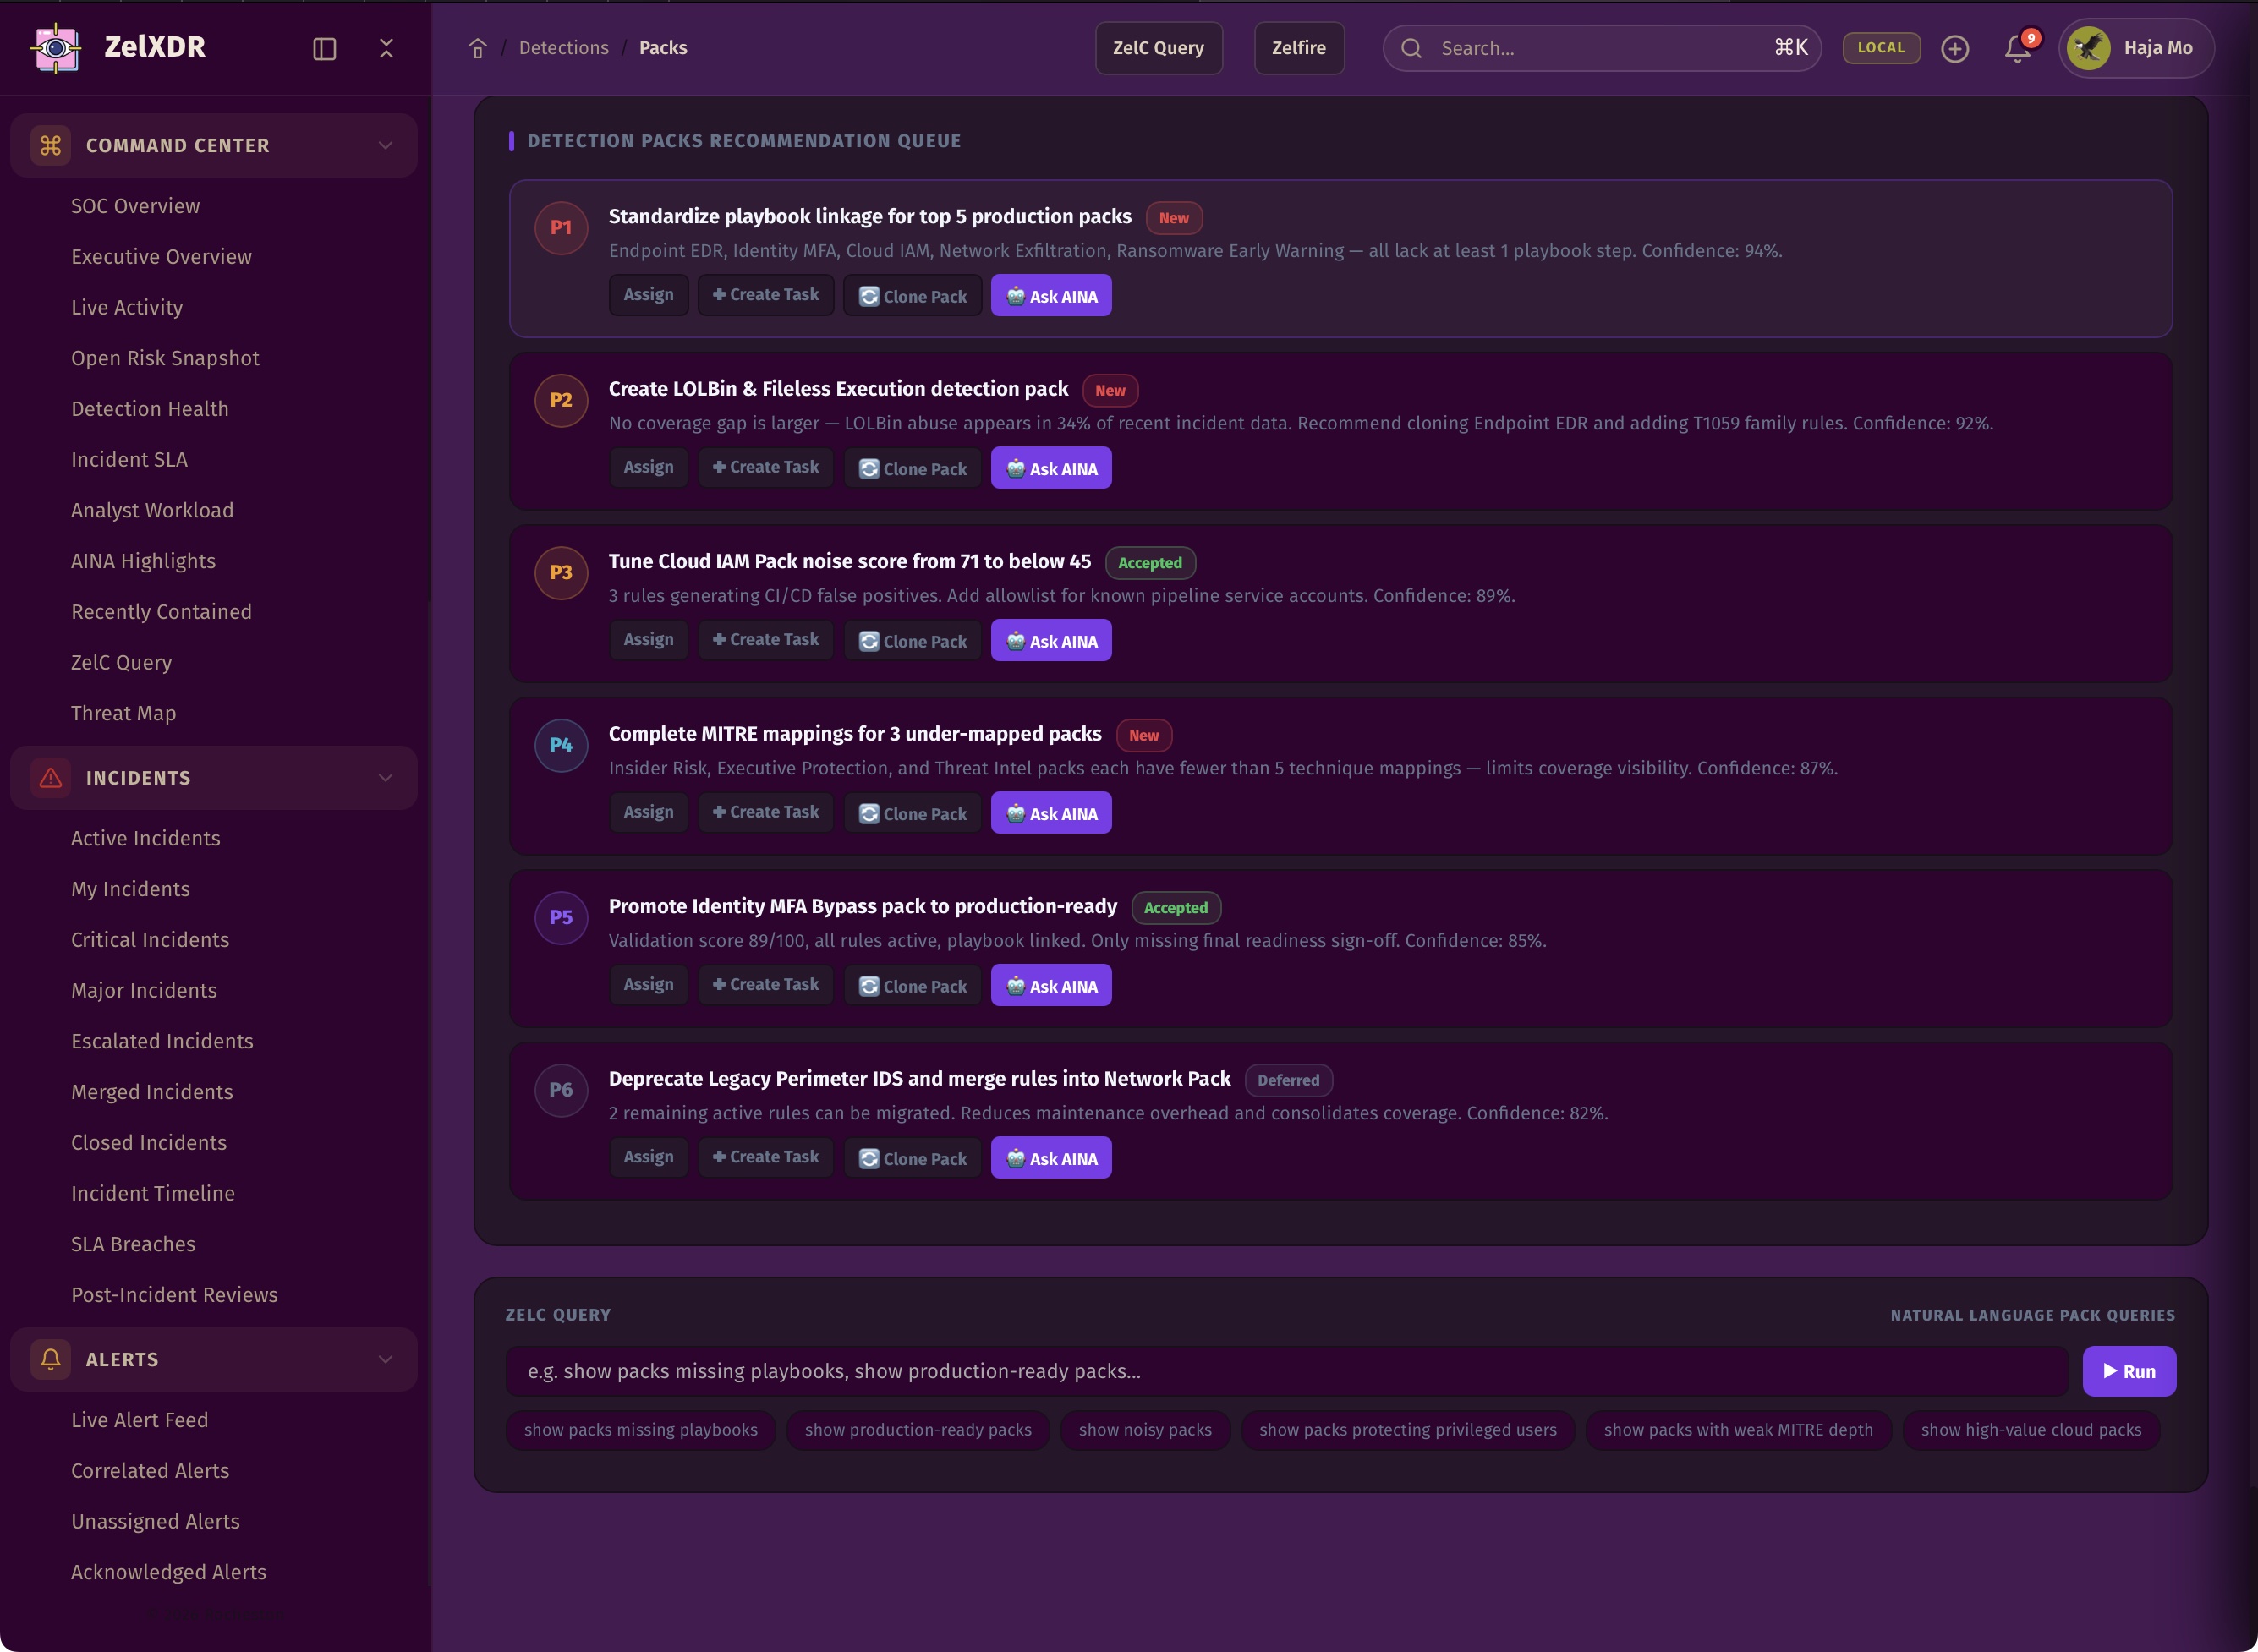
Detection Packs bundle rules, mappings, playbooks, scoring, and context into reusable deployment units that help teams scale good detection engineering across environments.
A strong pack is reusable security discipline.
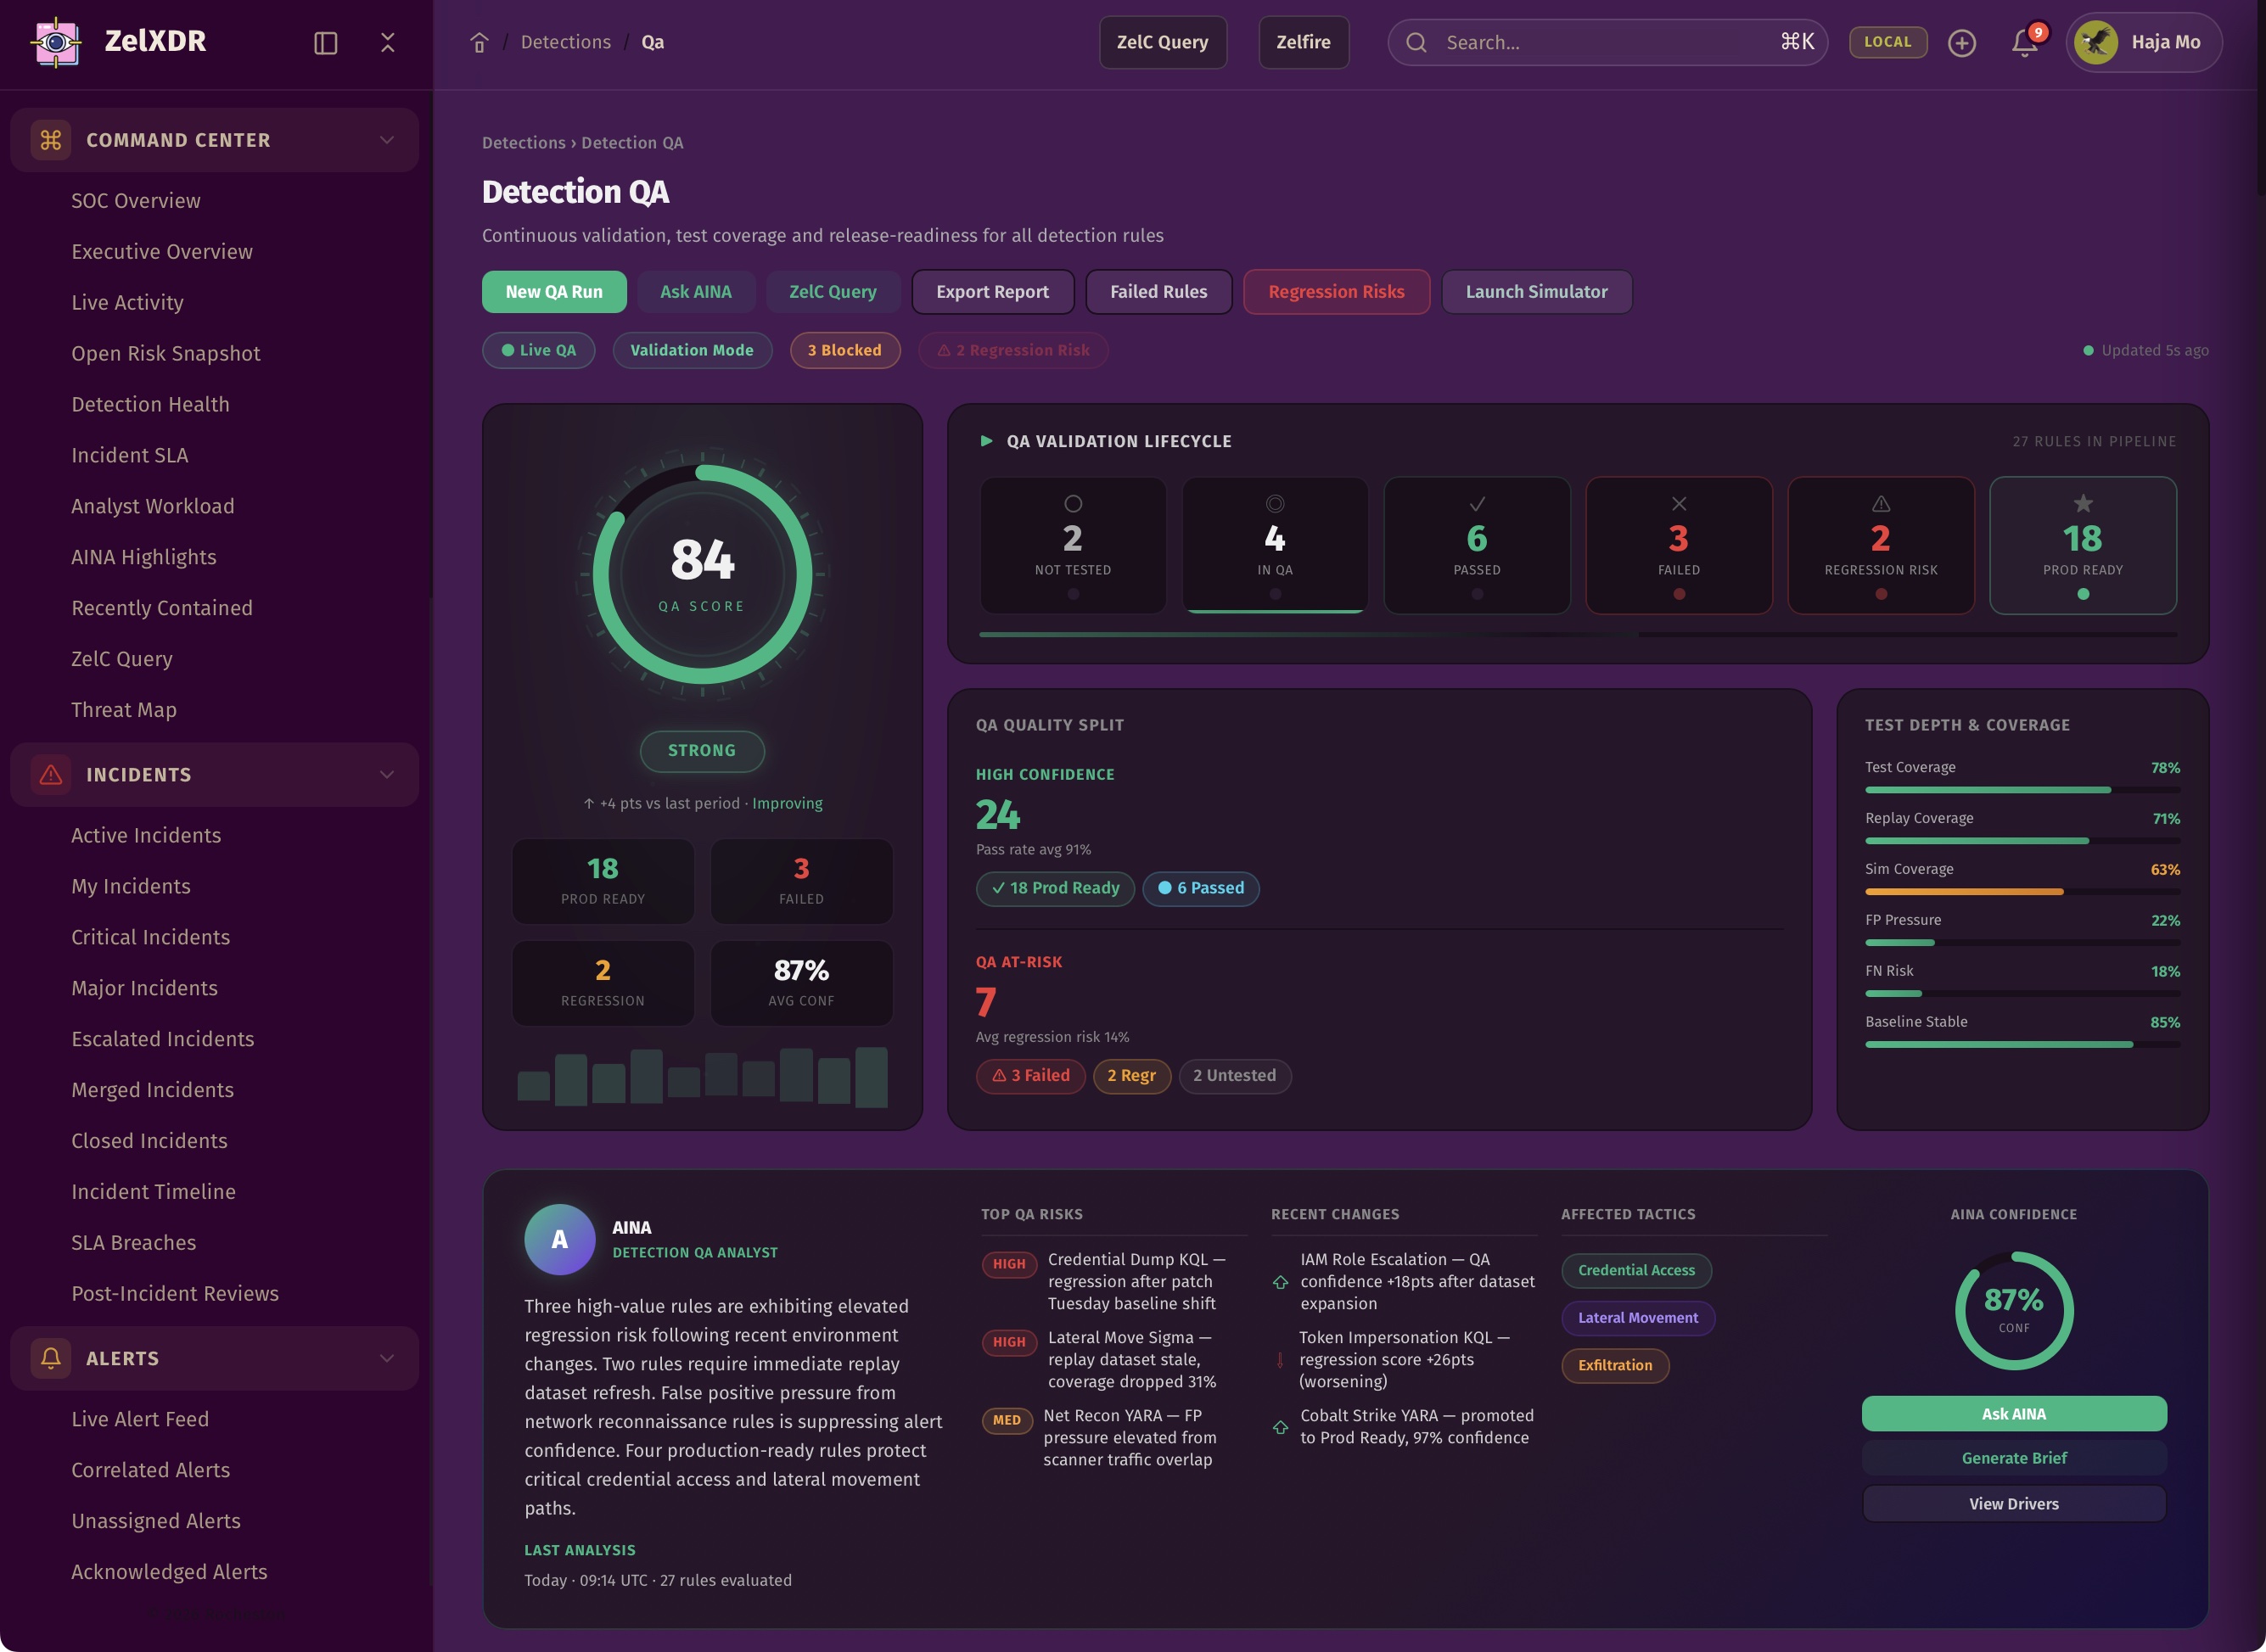
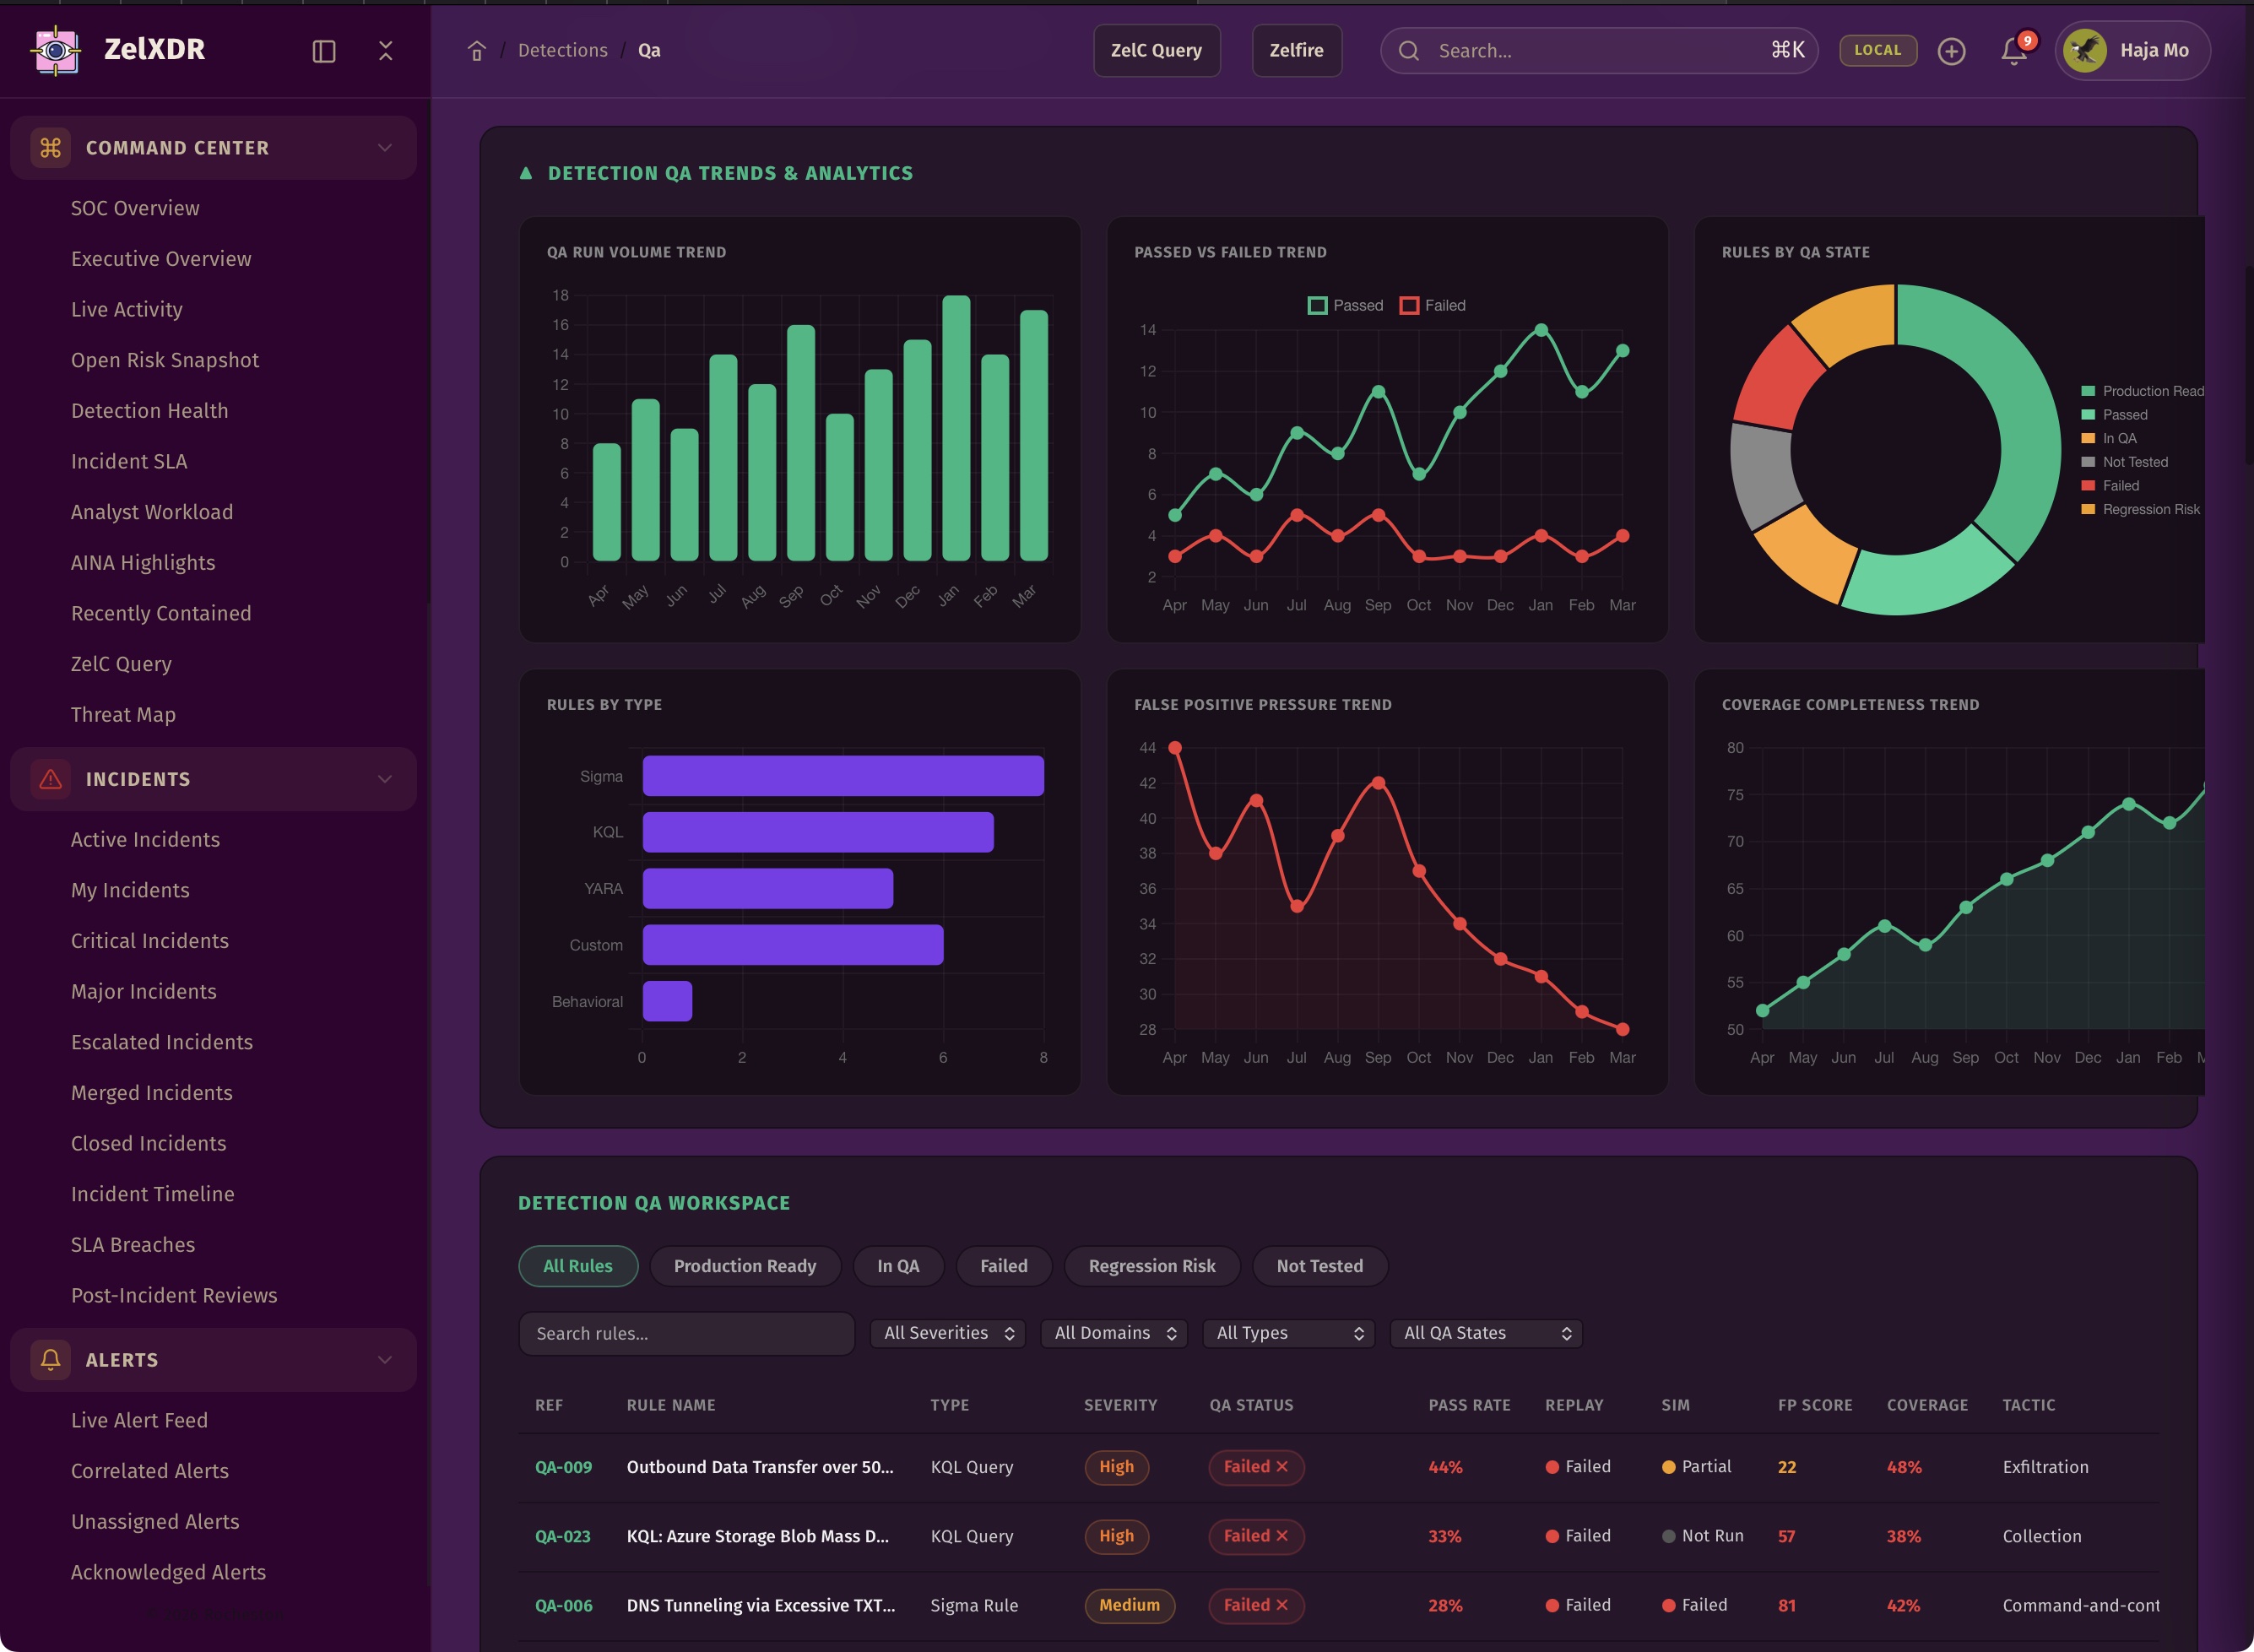
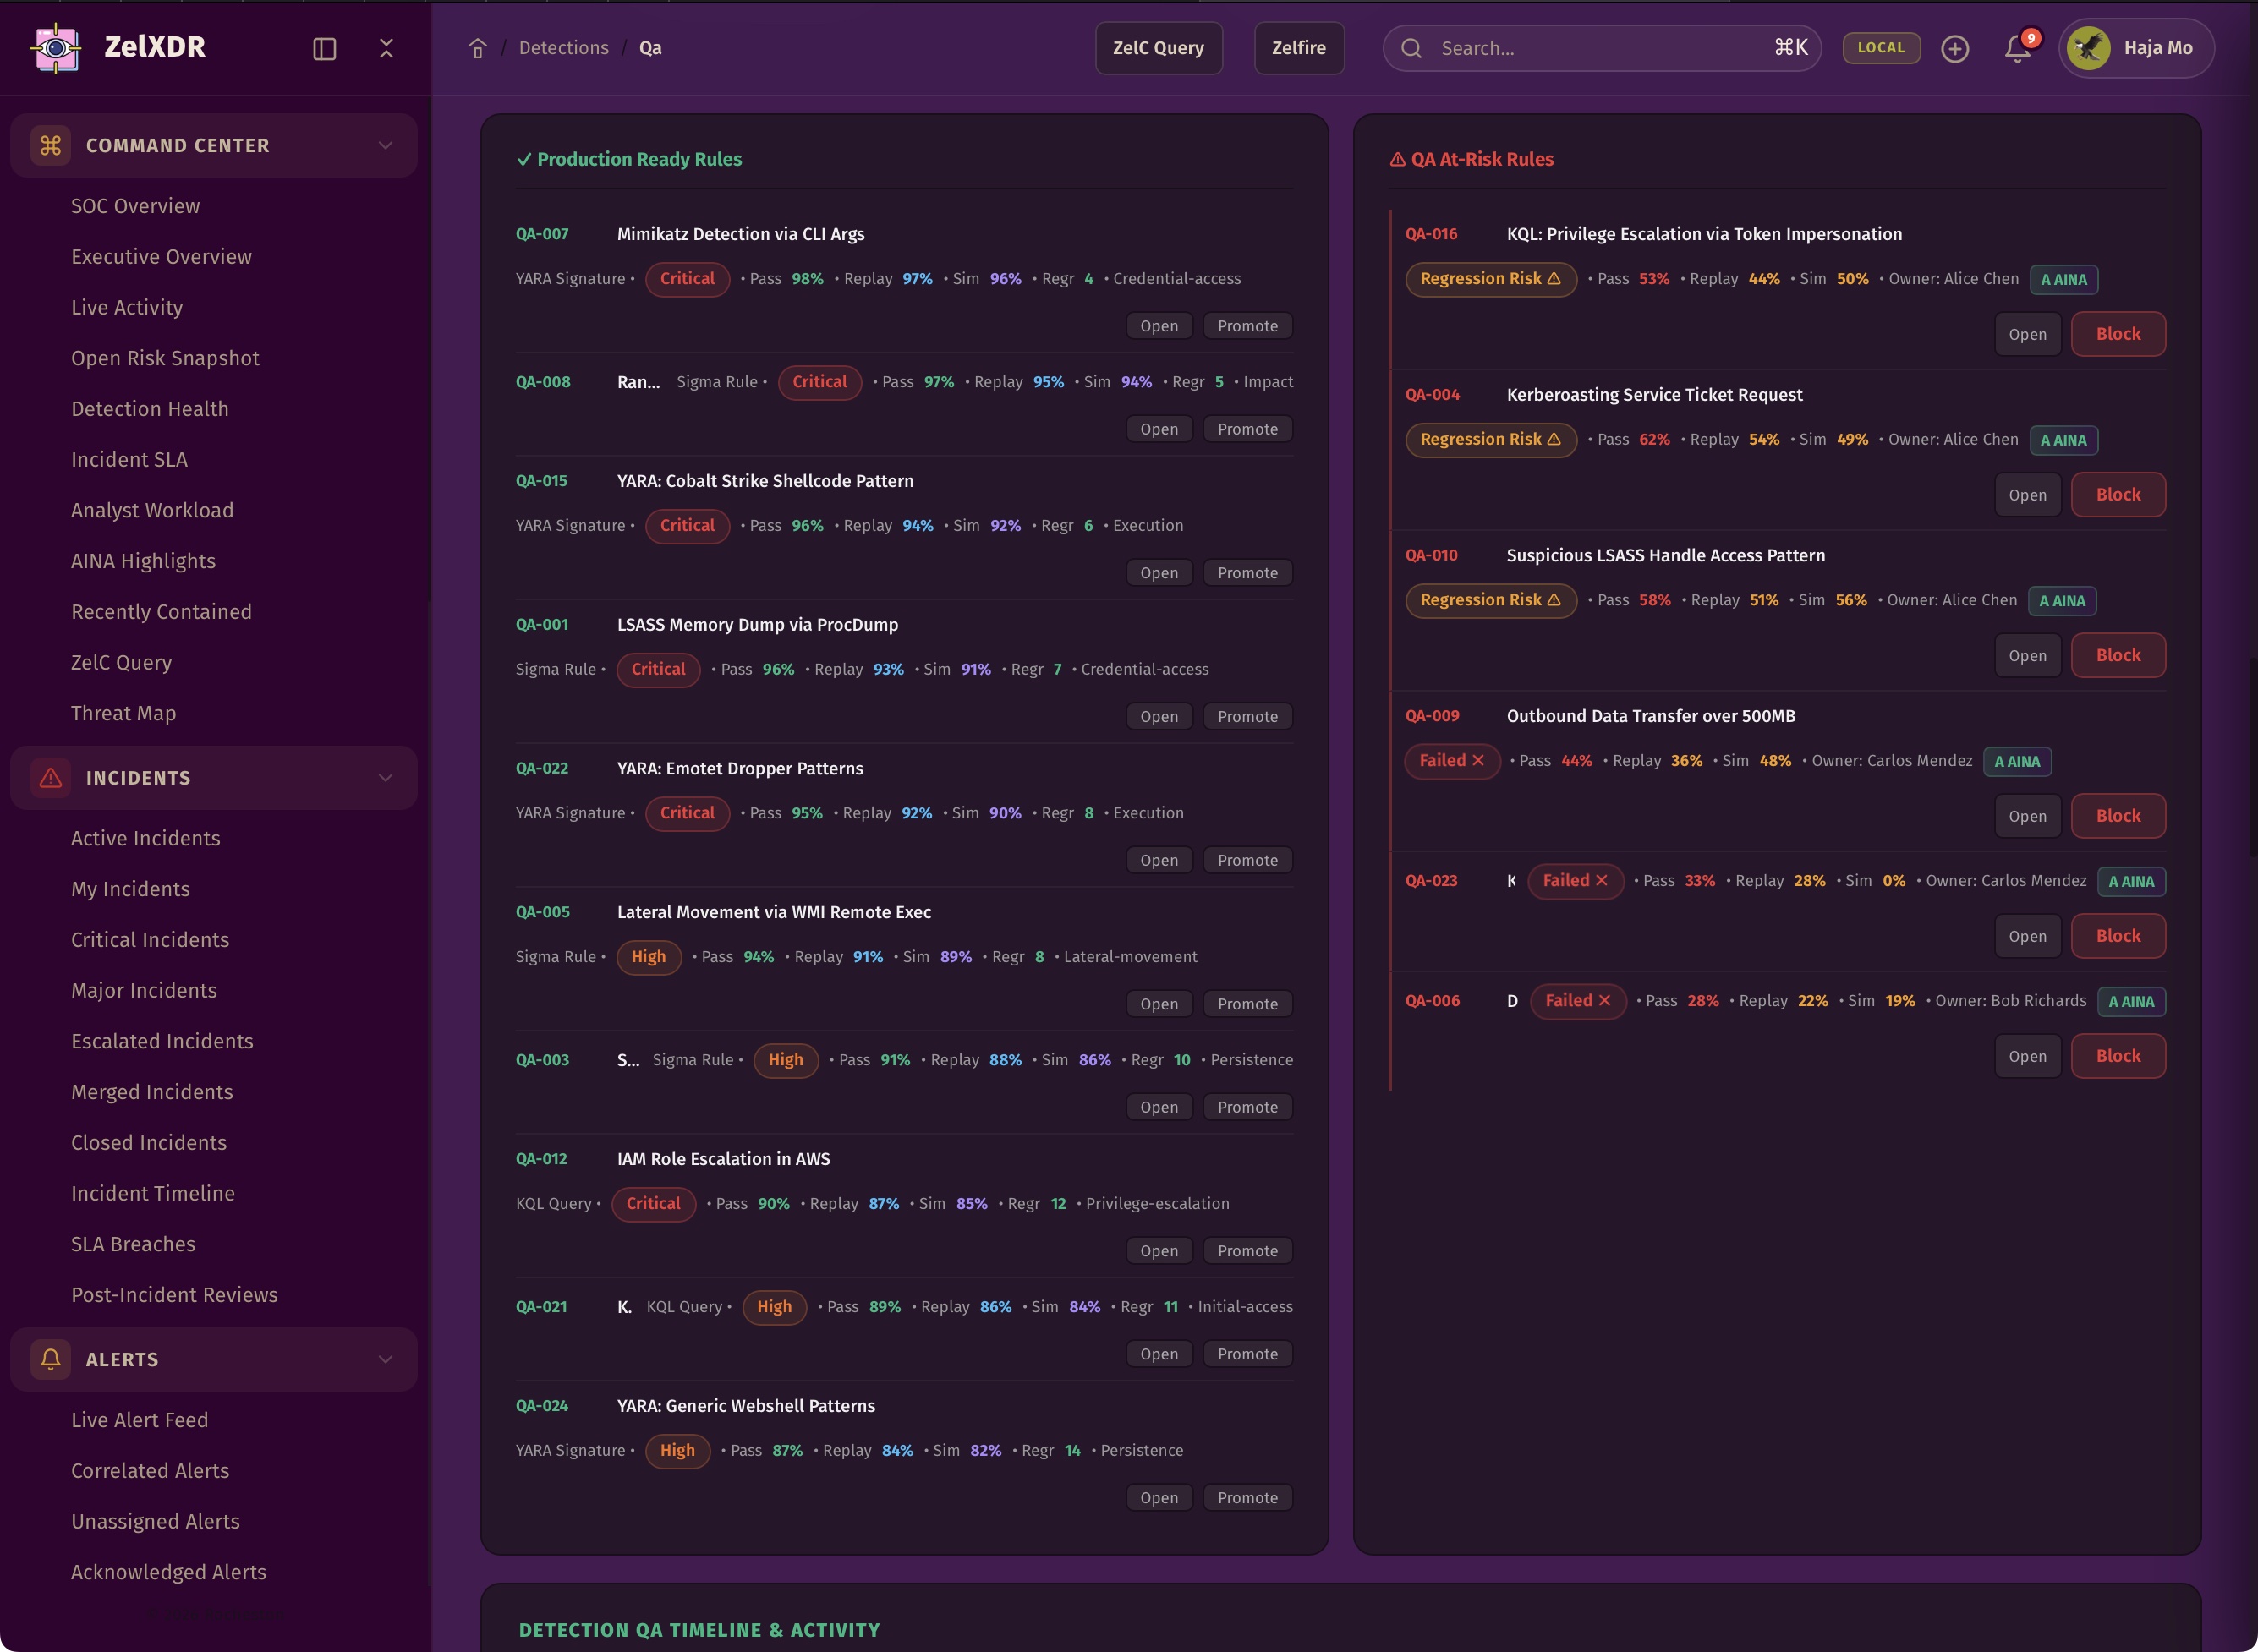
ZelXDR gives teams a way to validate detections through replay, simulation, testing, and regression review so production logic stays trustworthy over time.
Validation is what makes detection believable.
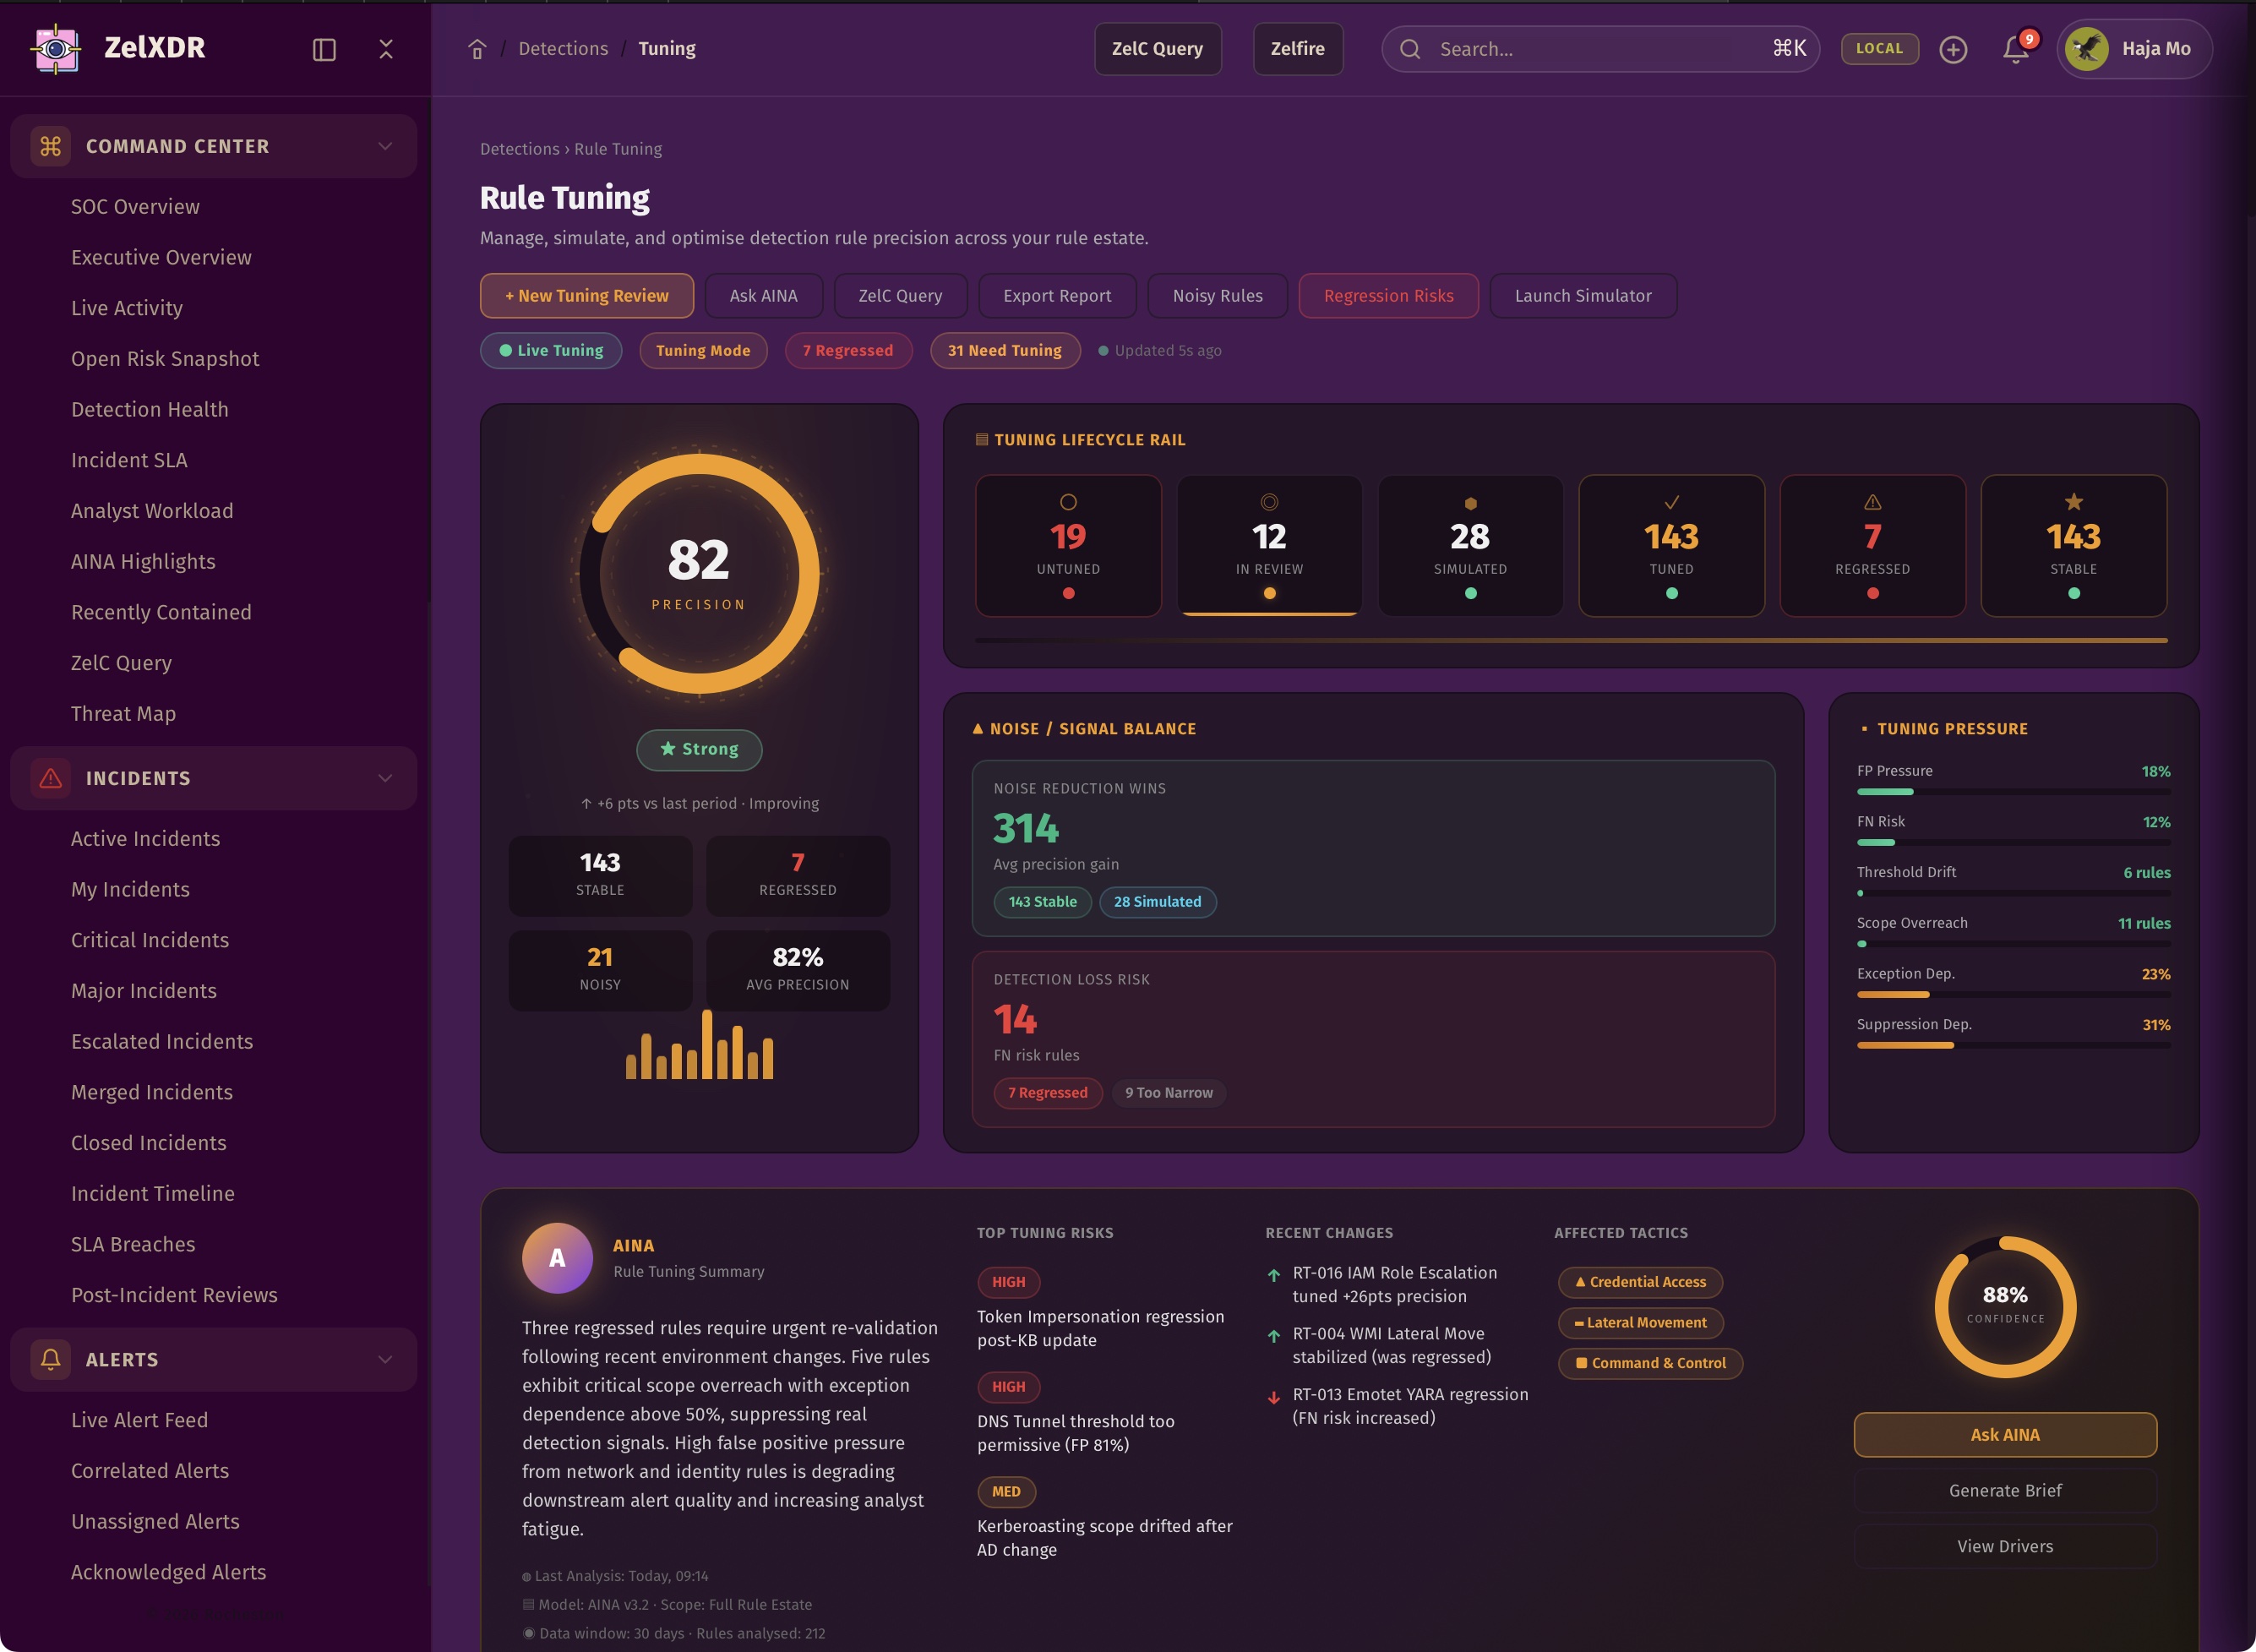
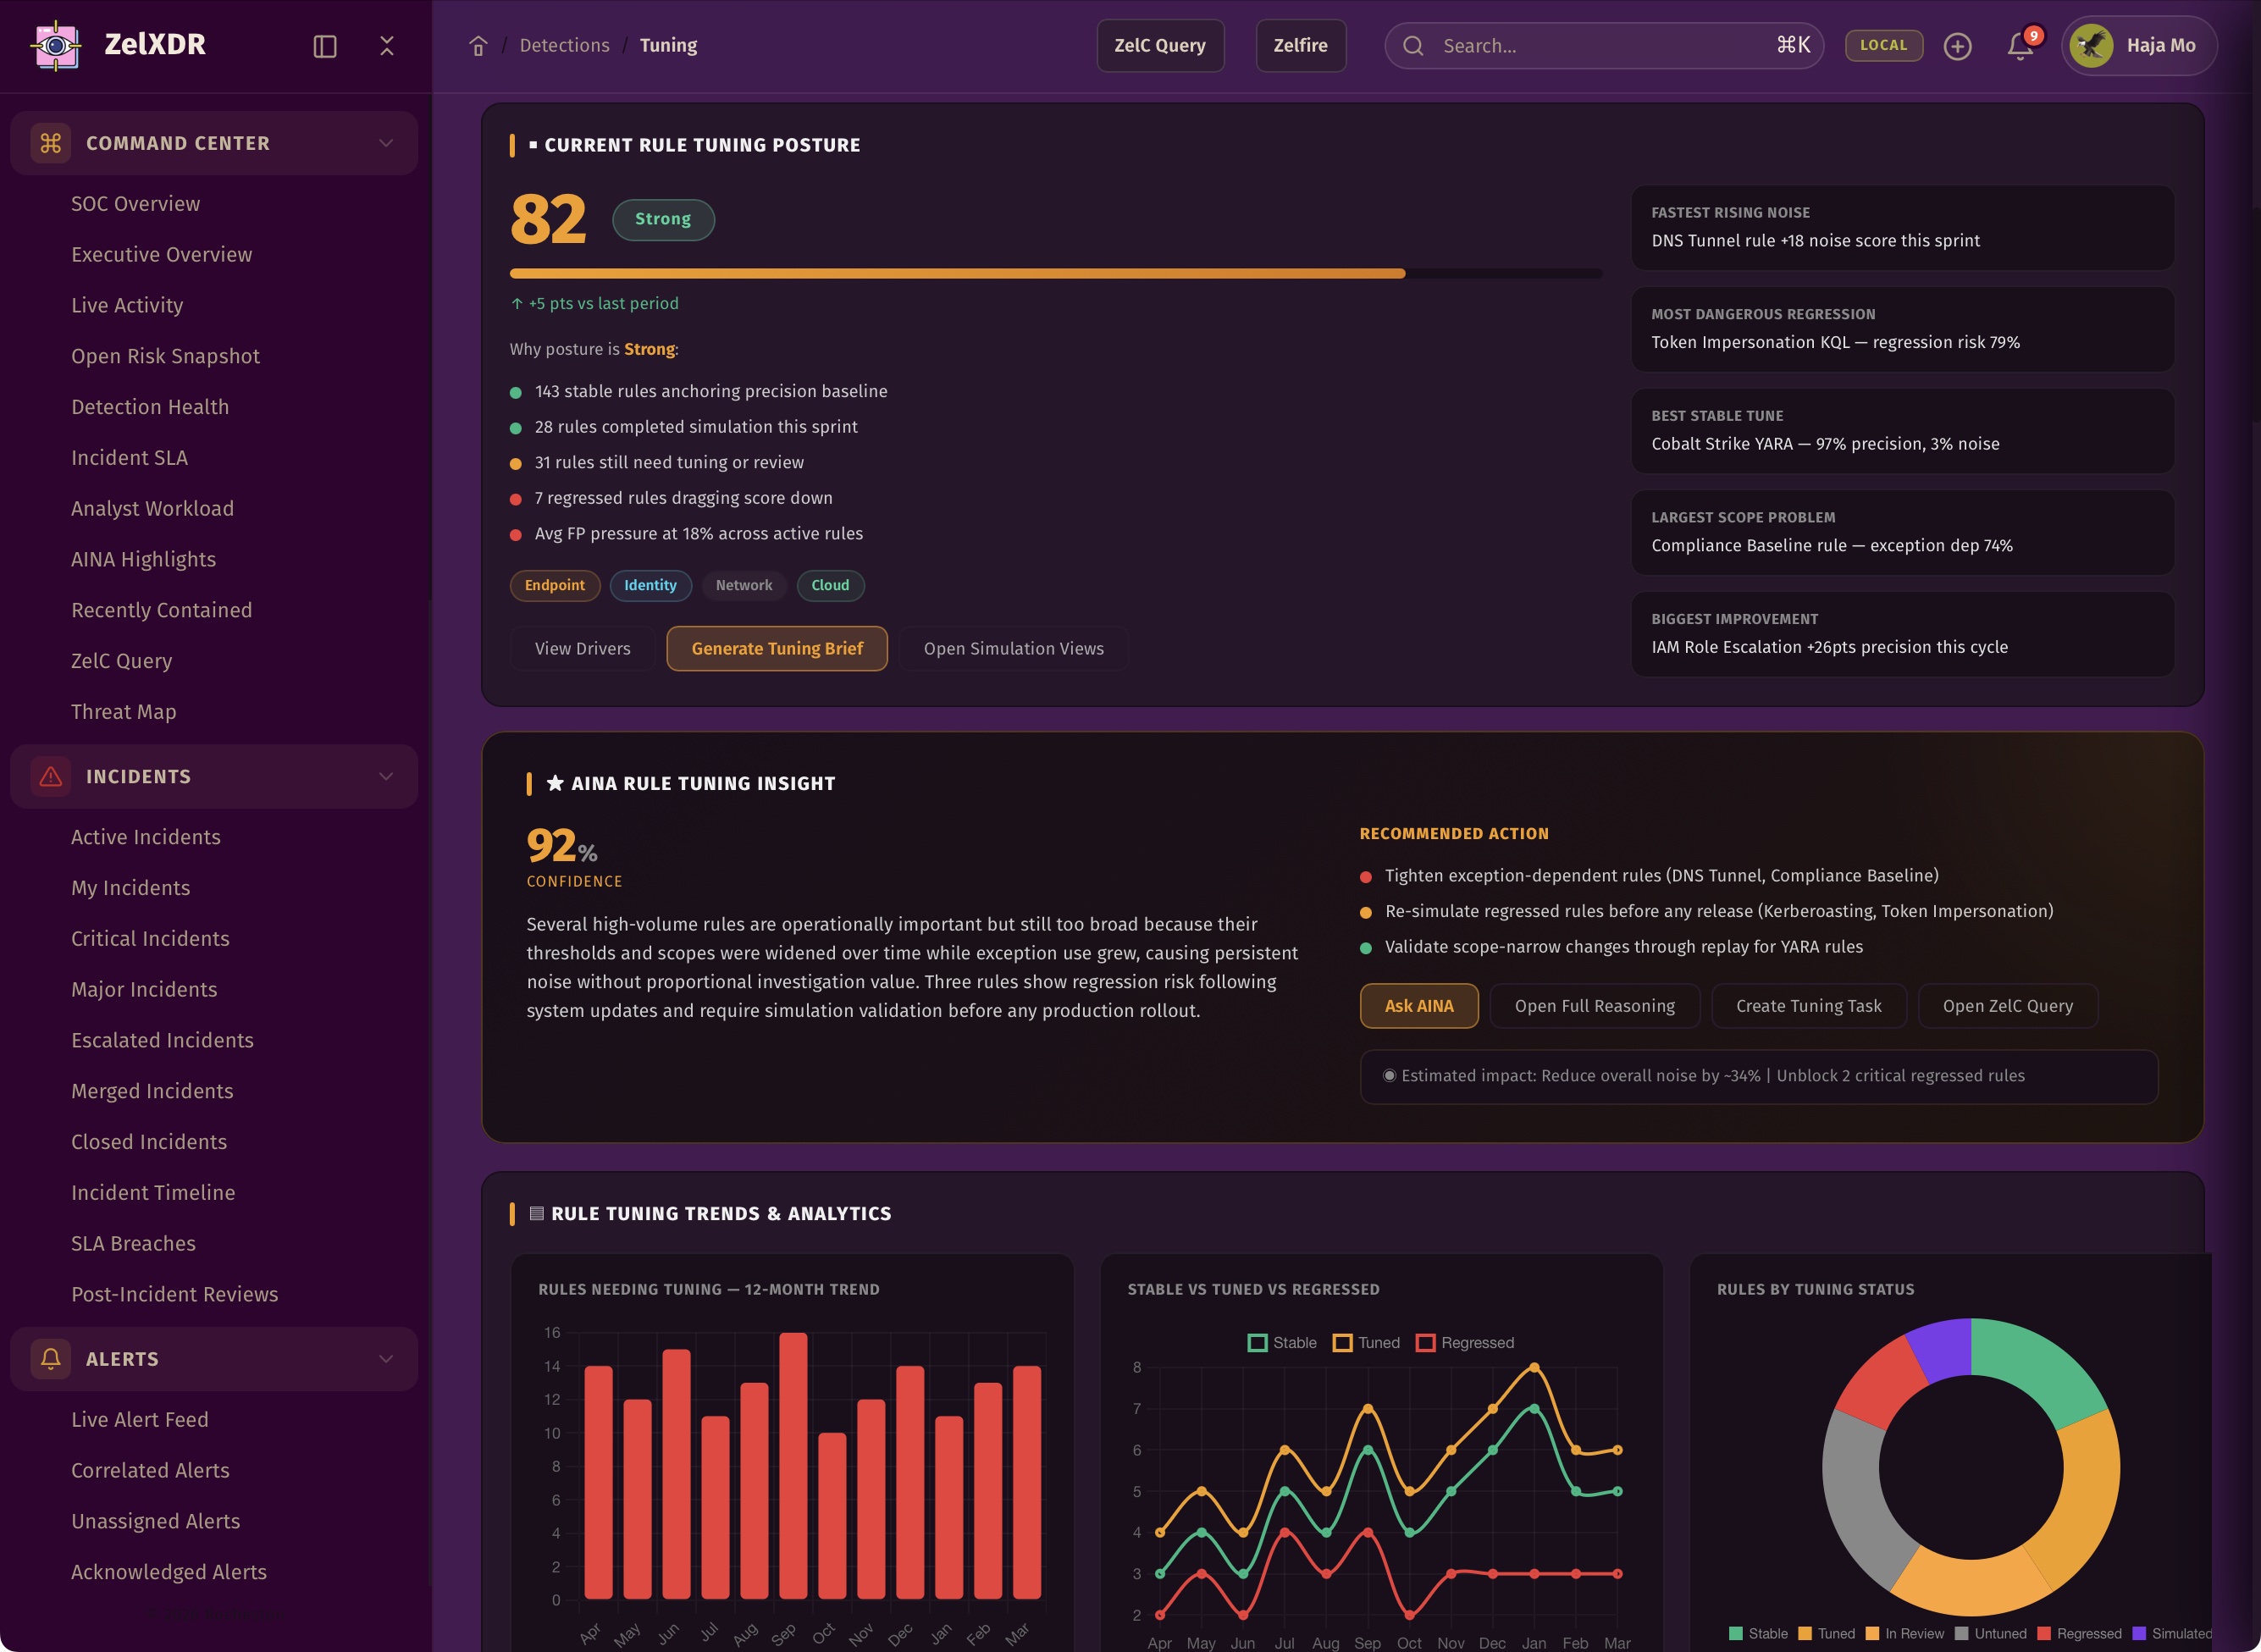
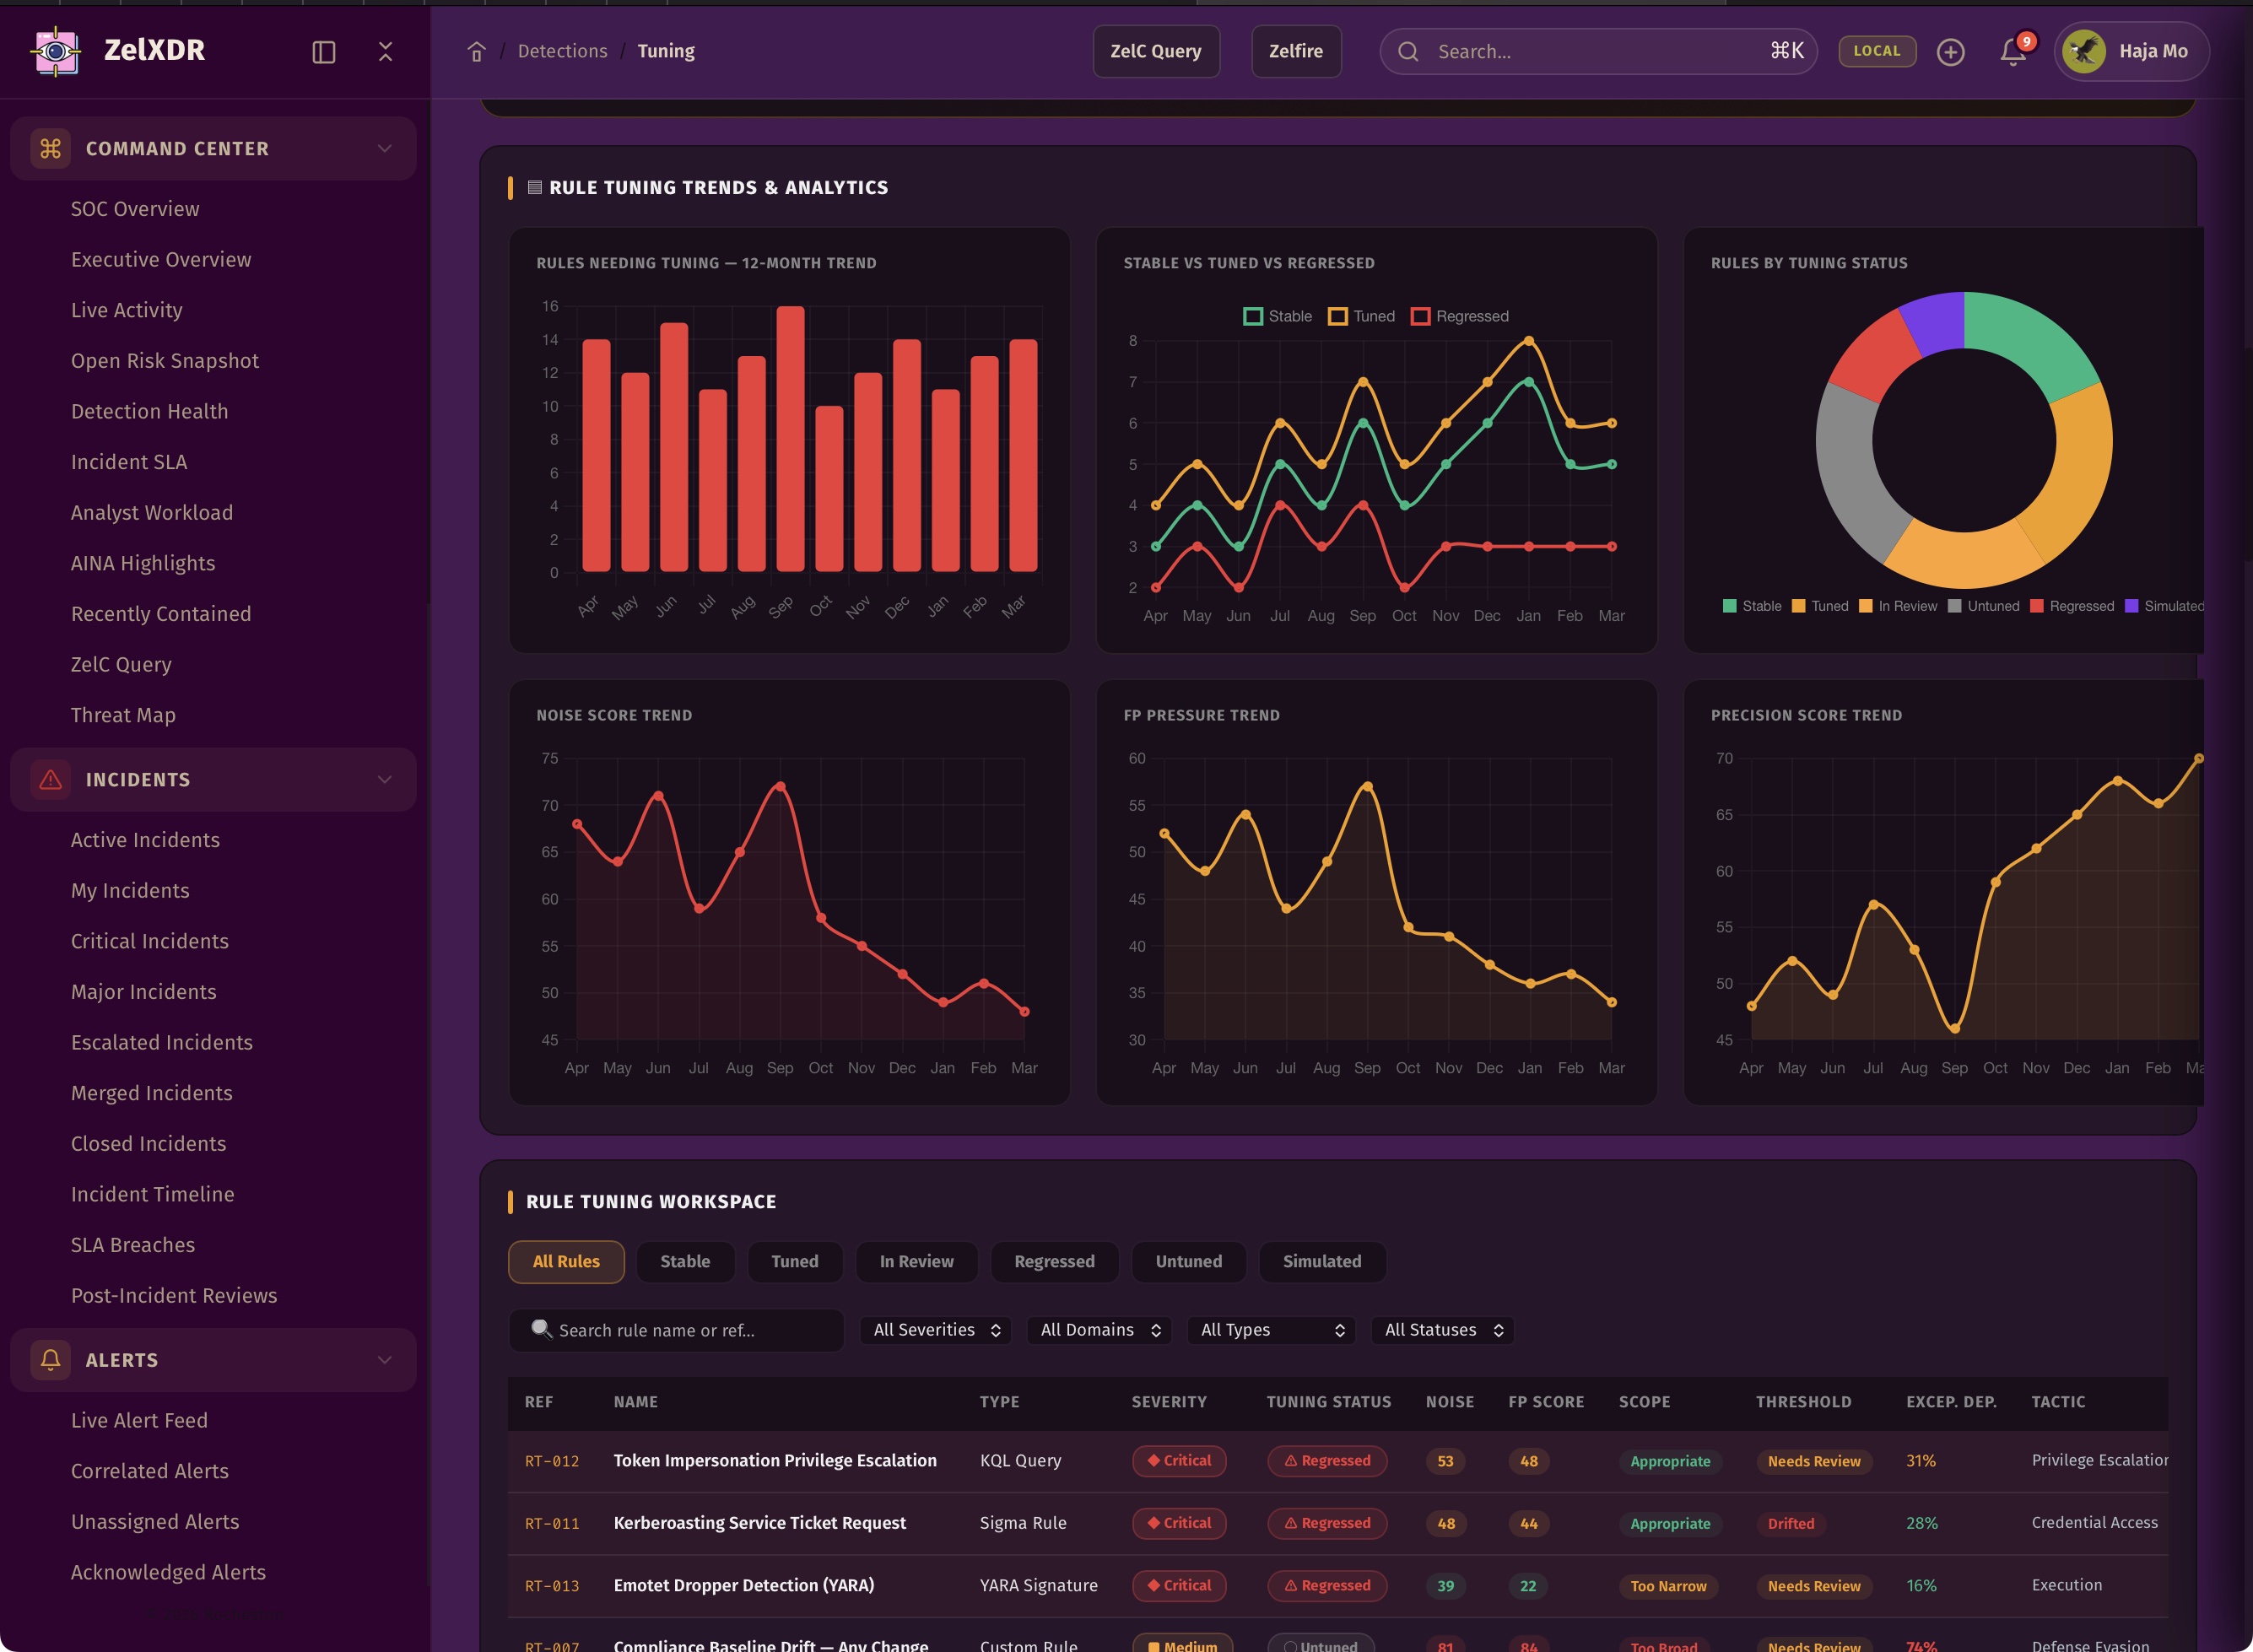
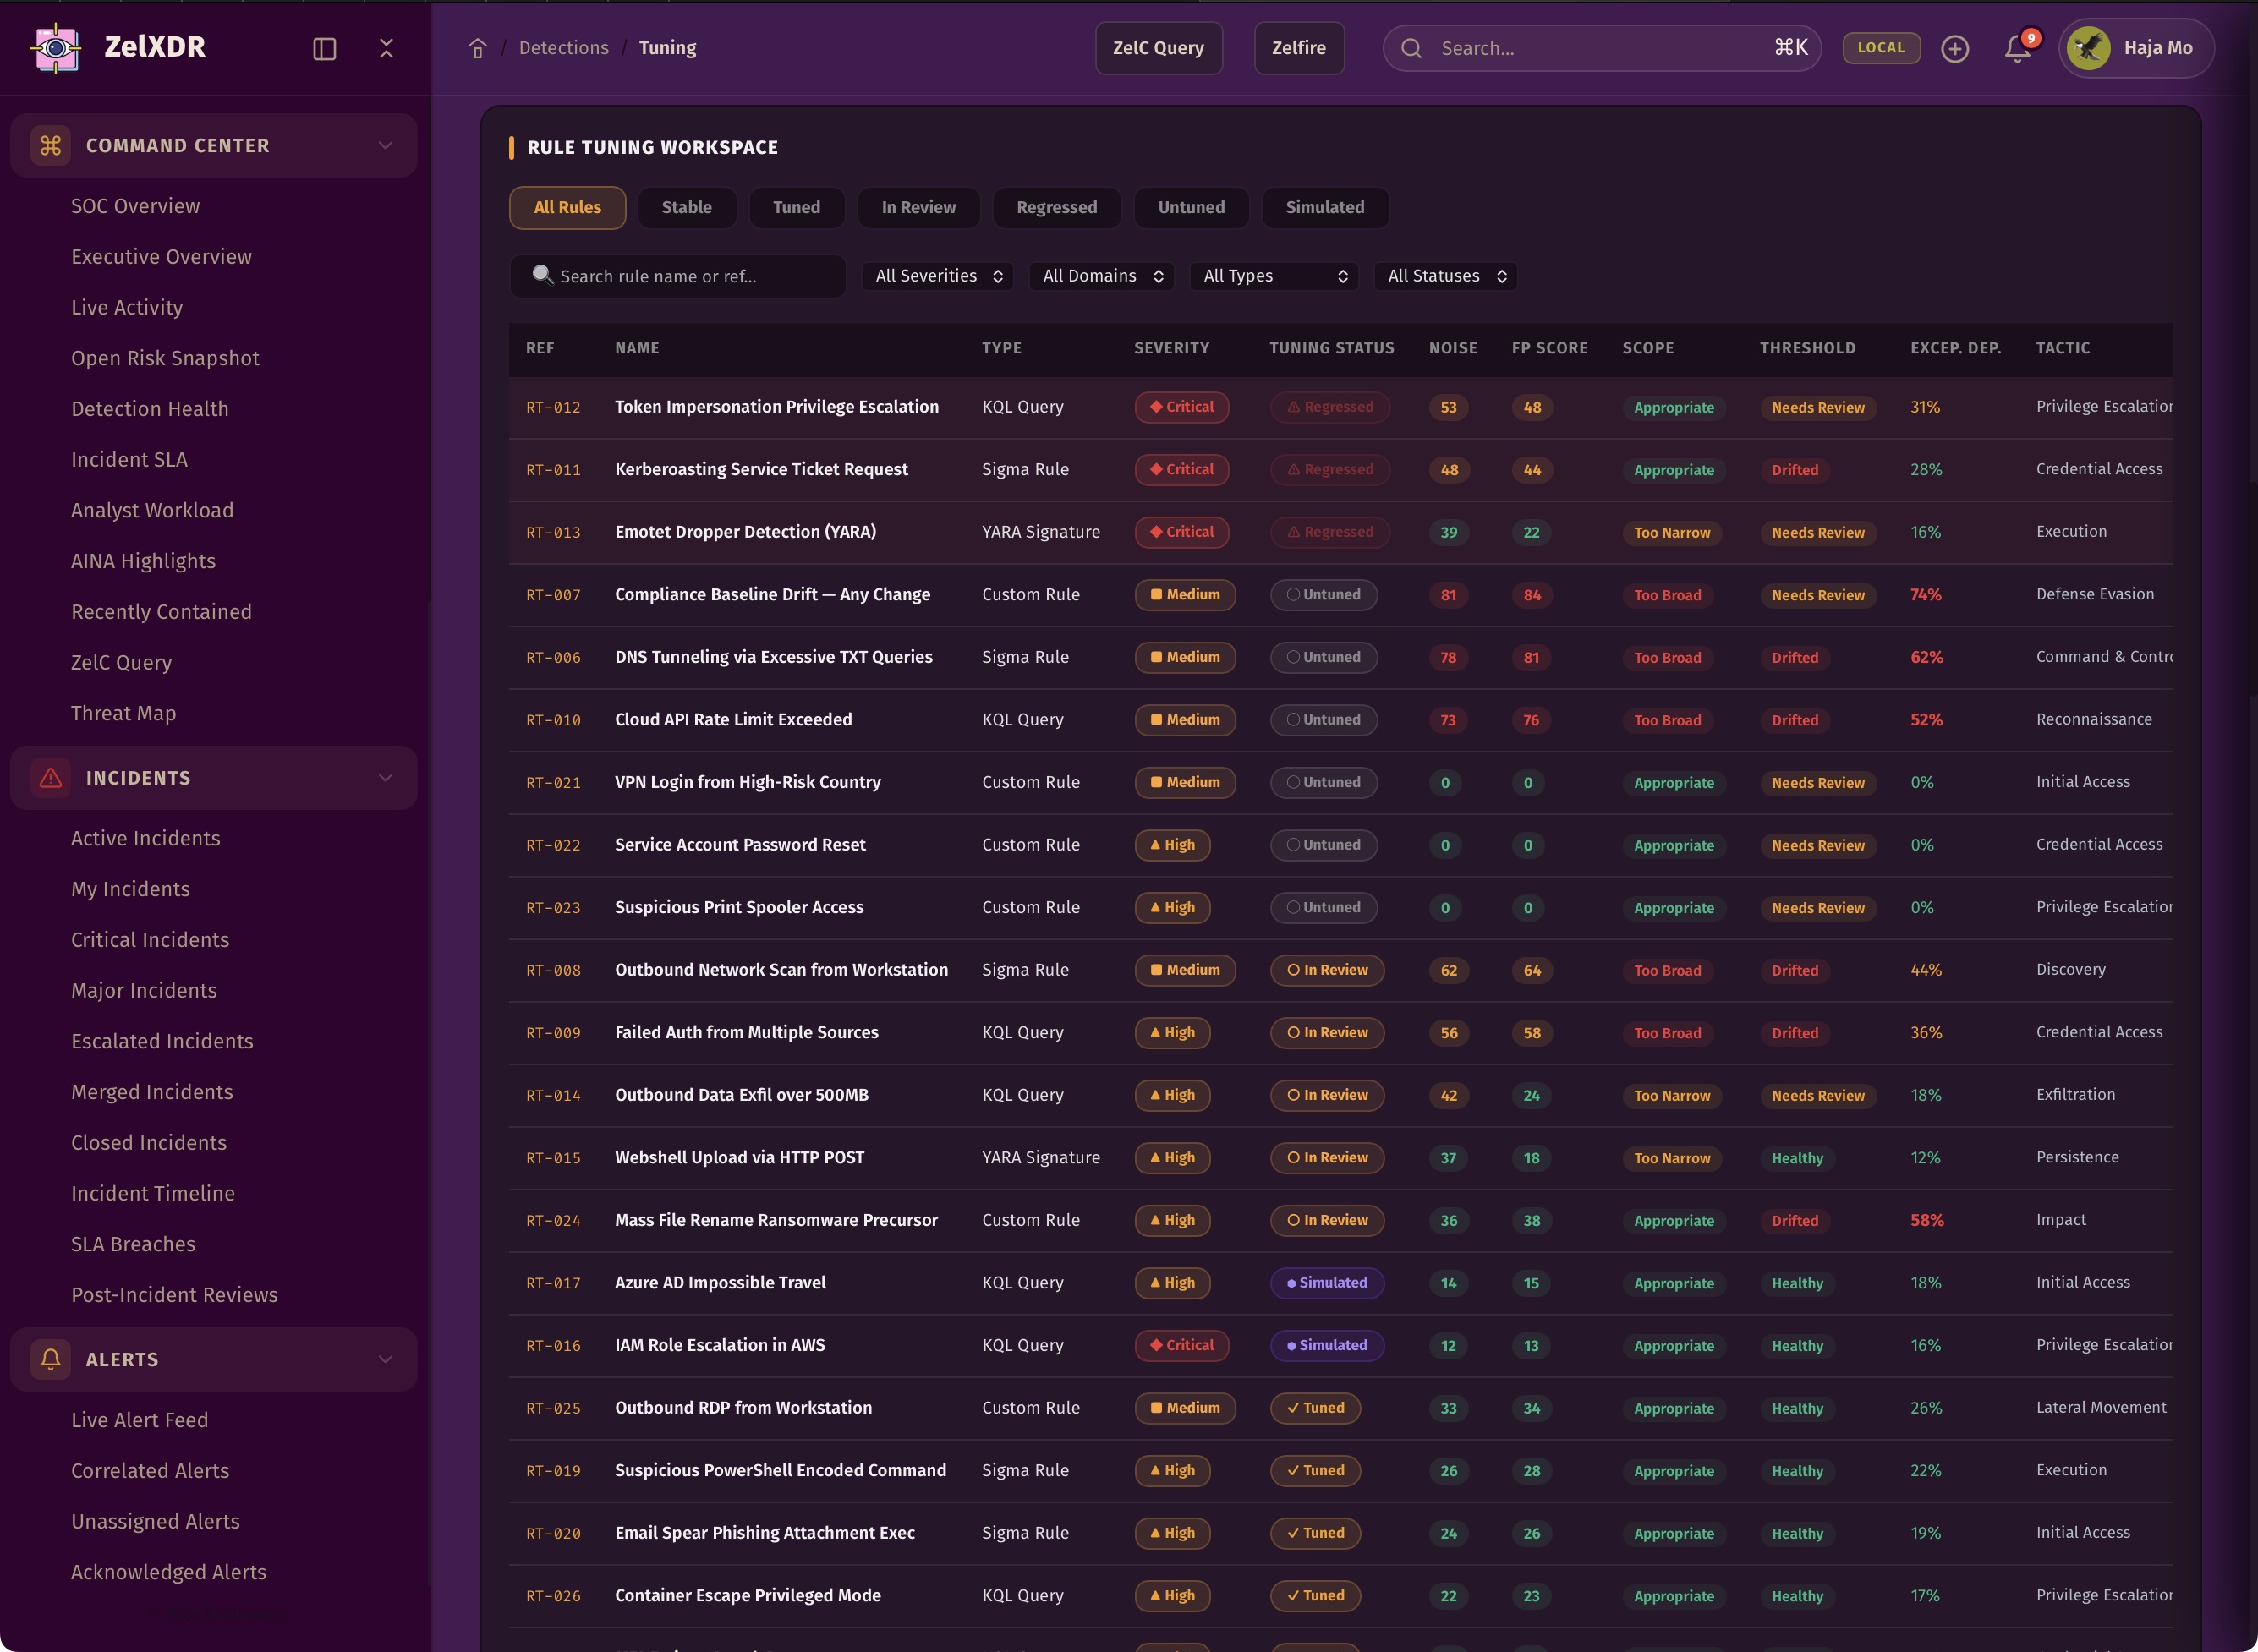
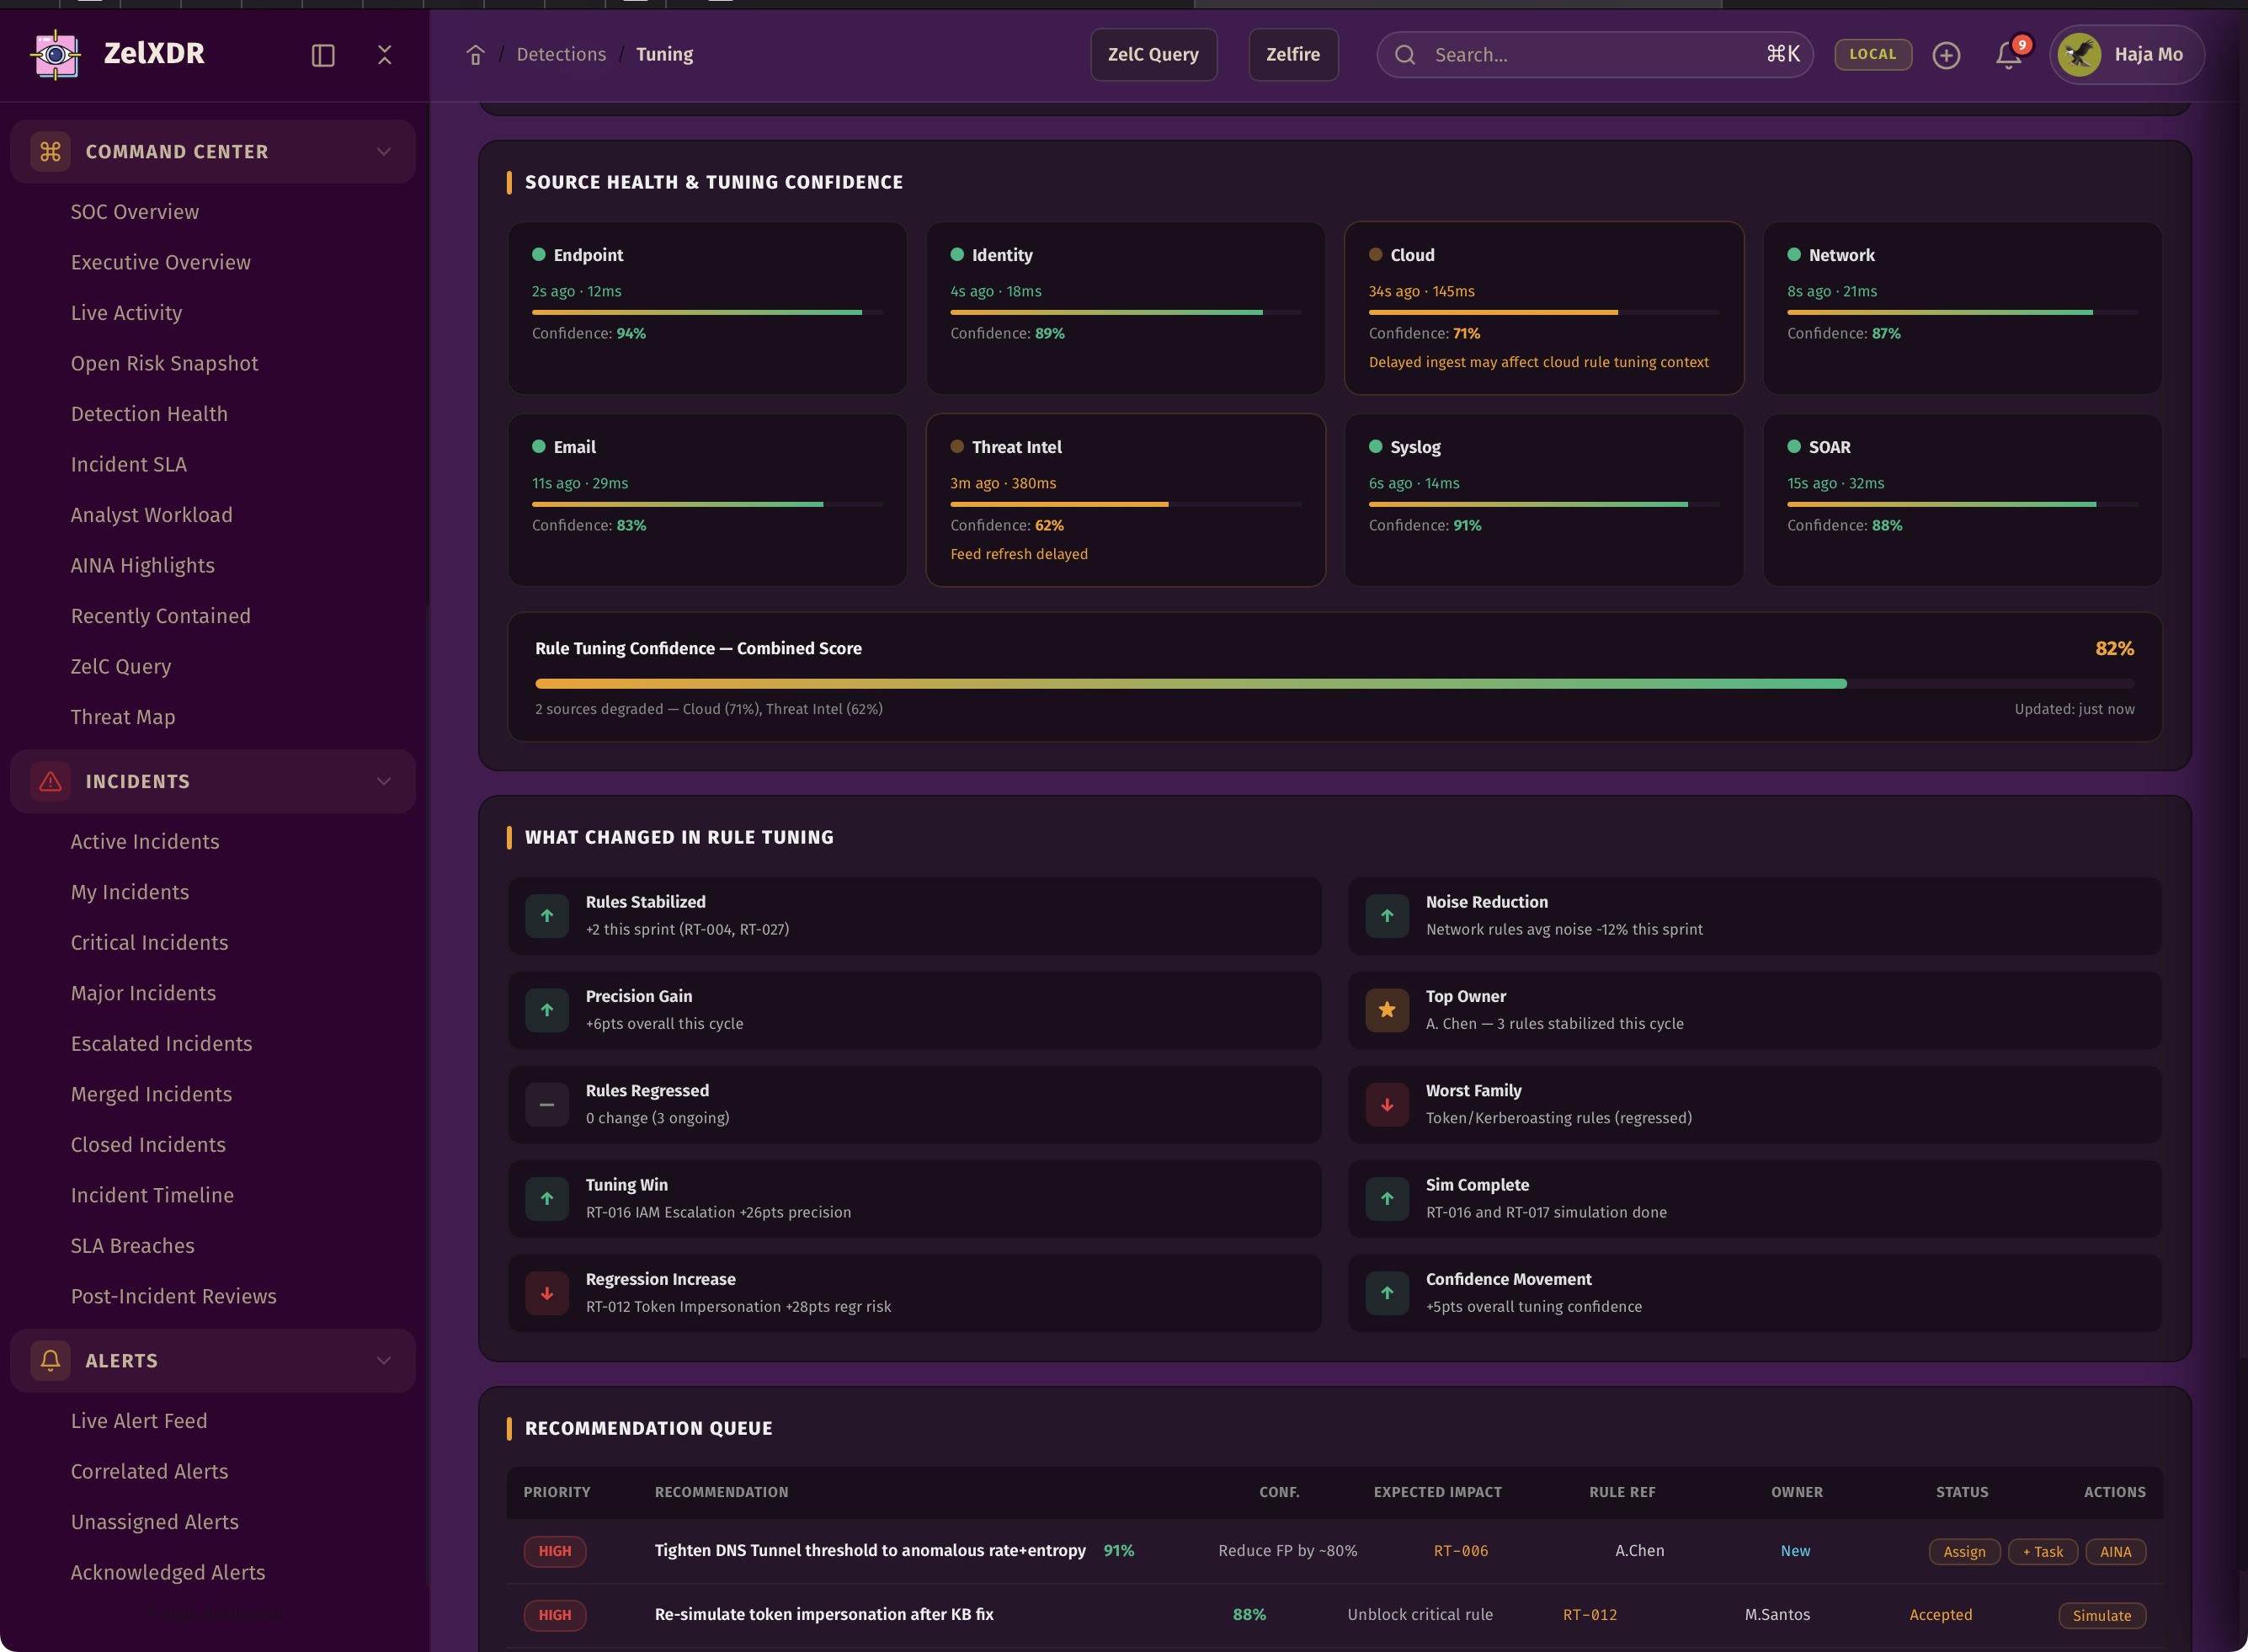
ZelXDR helps teams continuously narrow noise, reduce false positives, avoid blind spots, and measure the impact of every tuning decision across the security stack.
Precision is built through tuning, not luck.
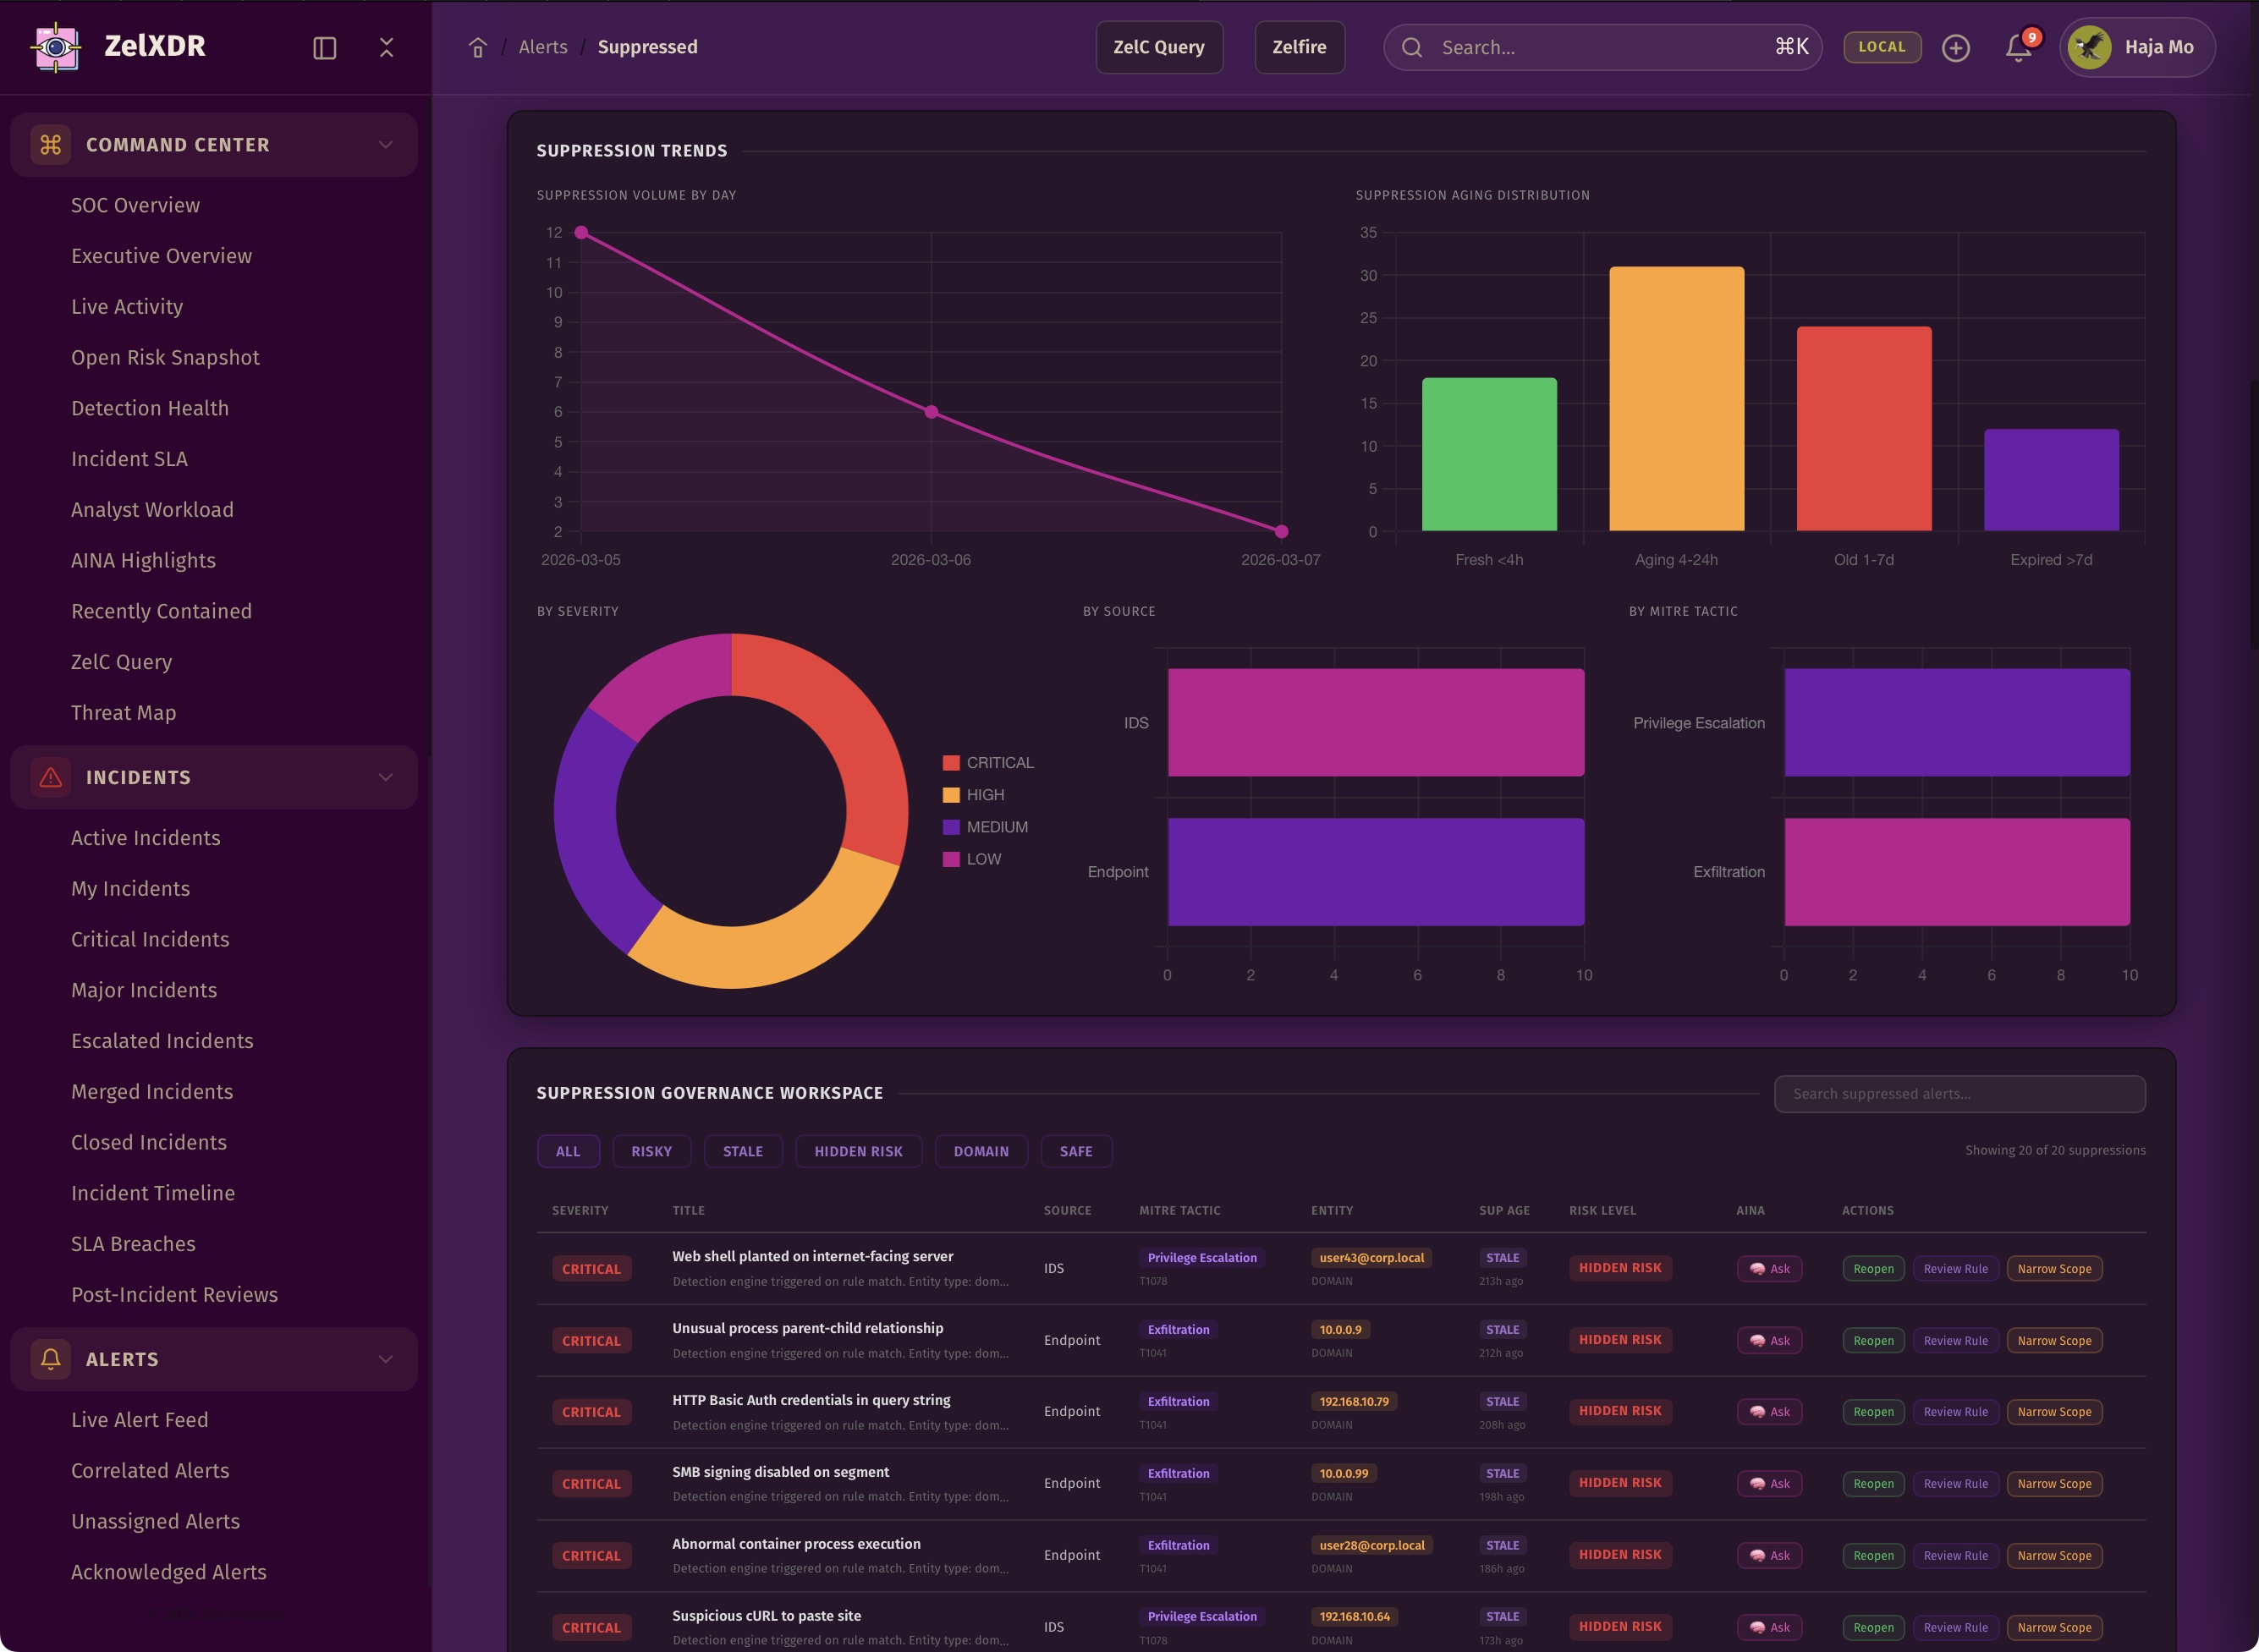
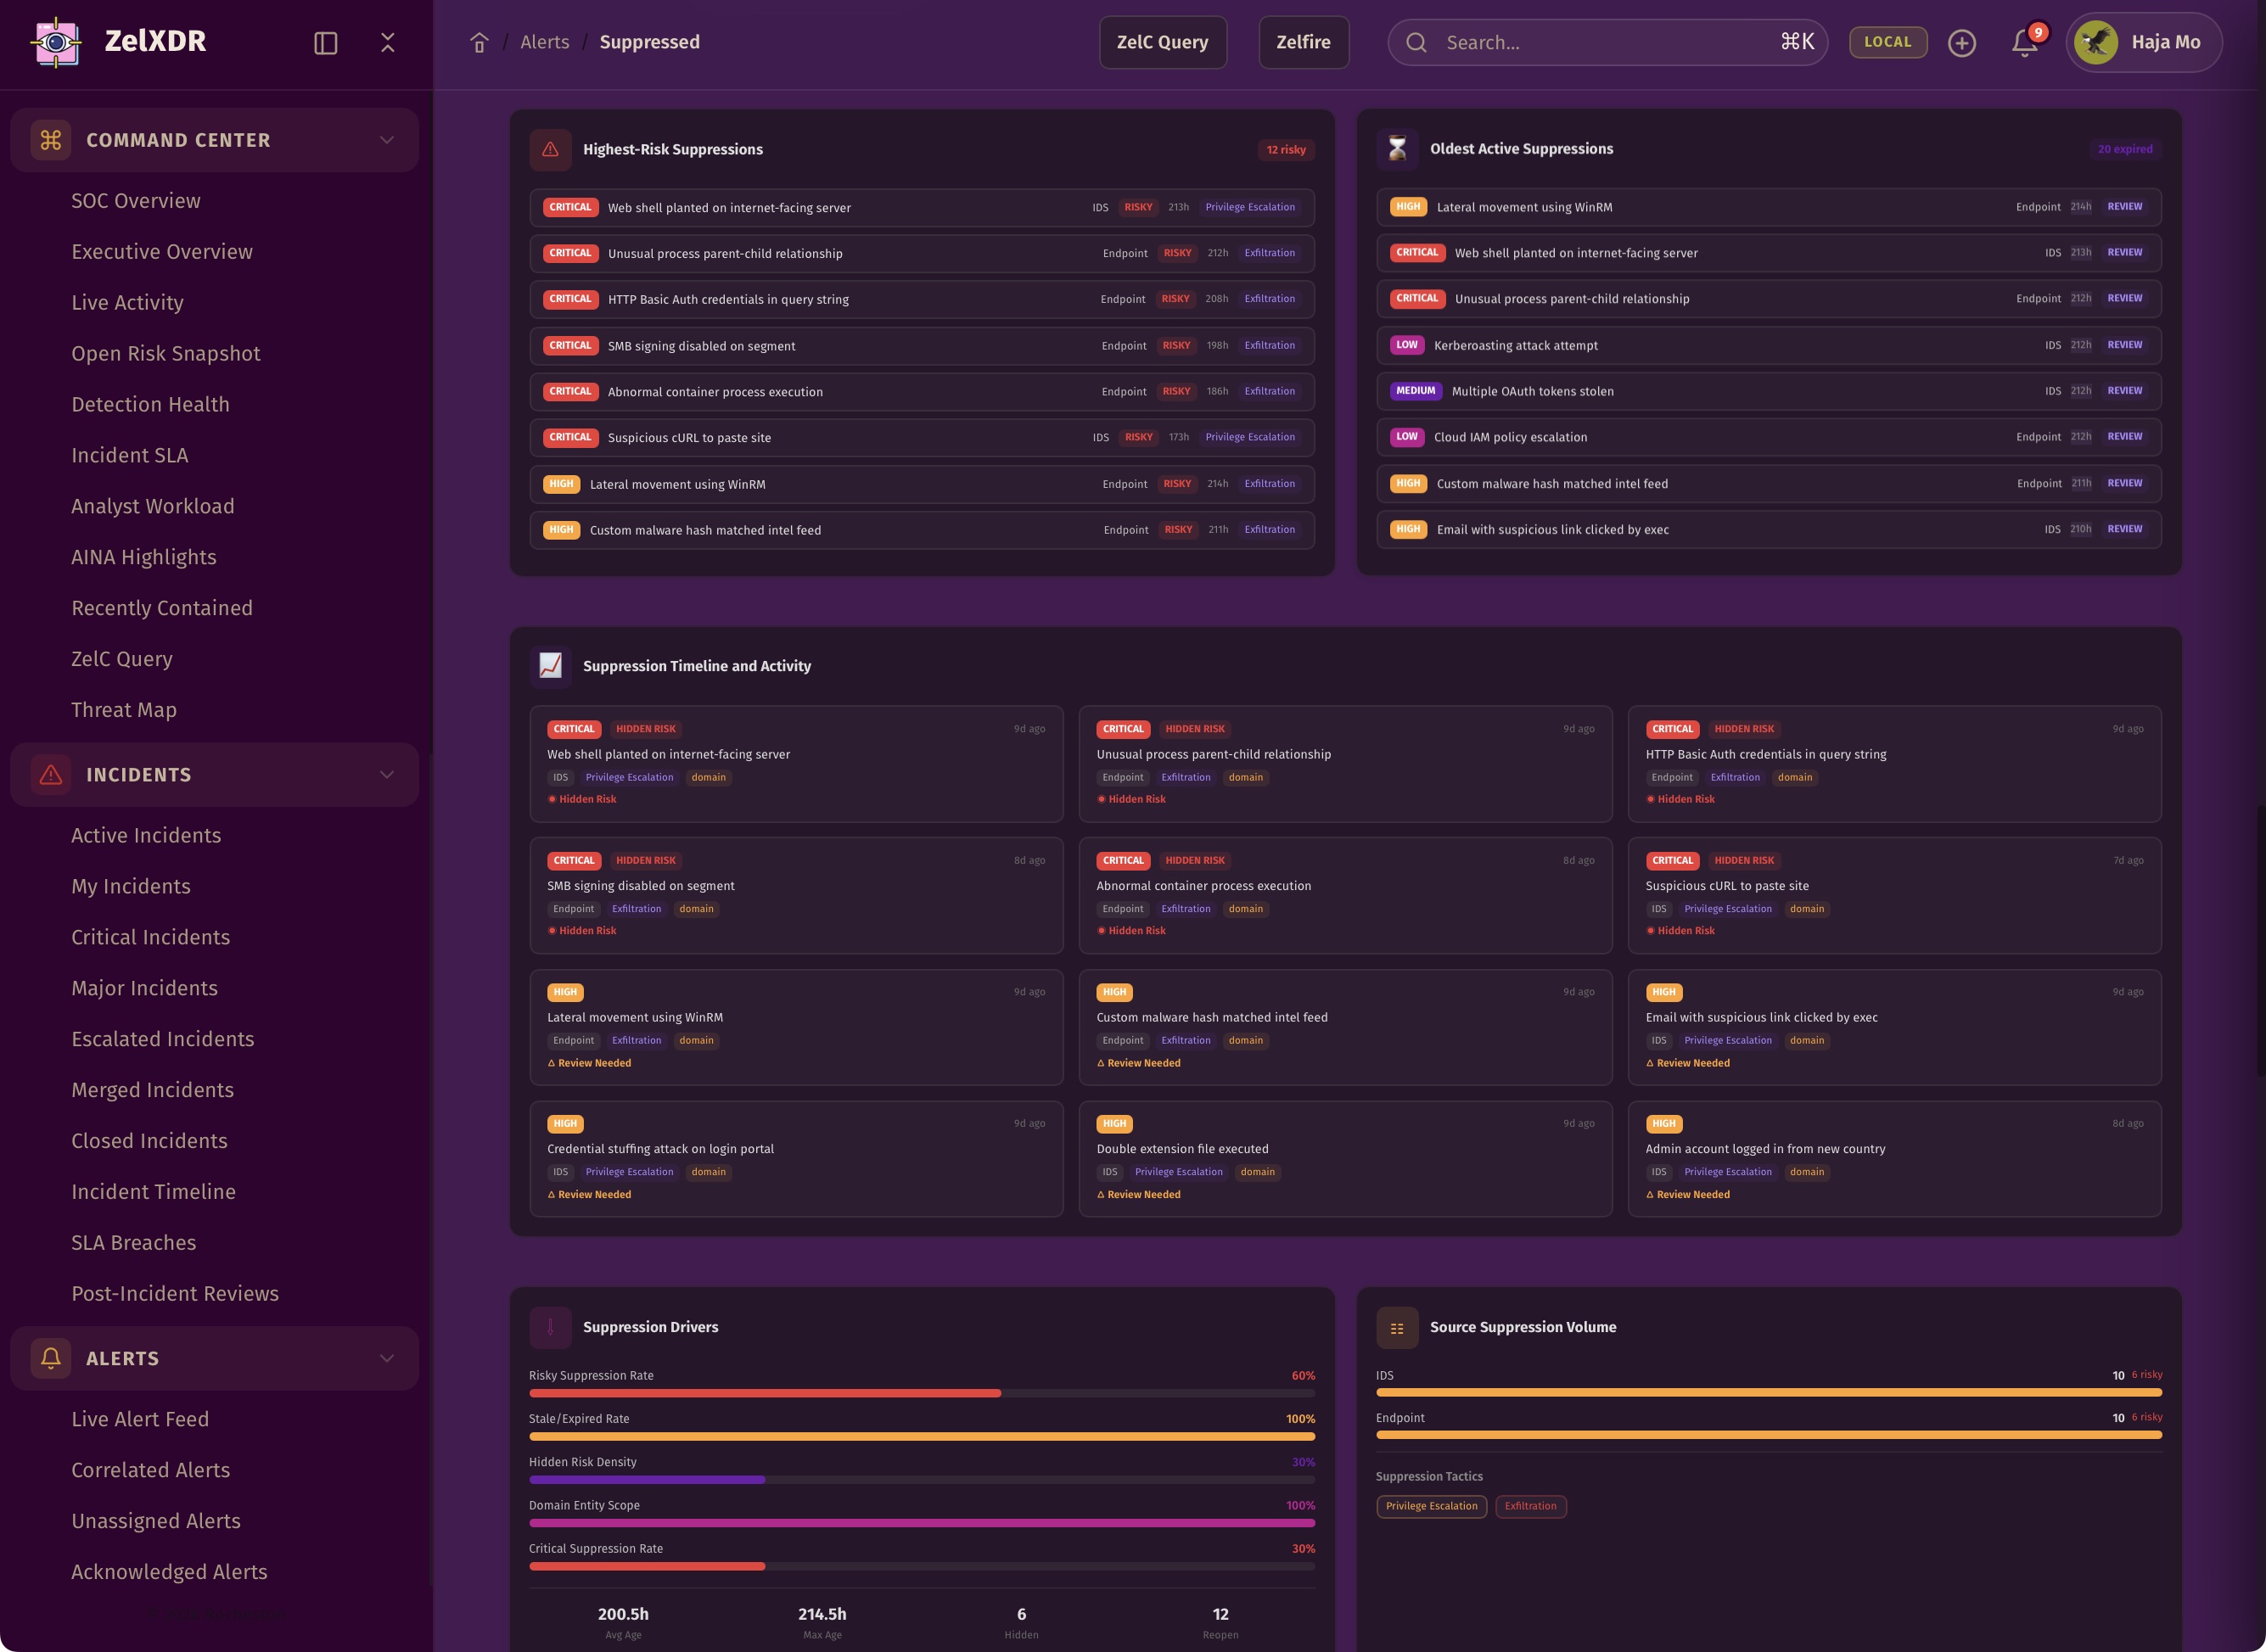
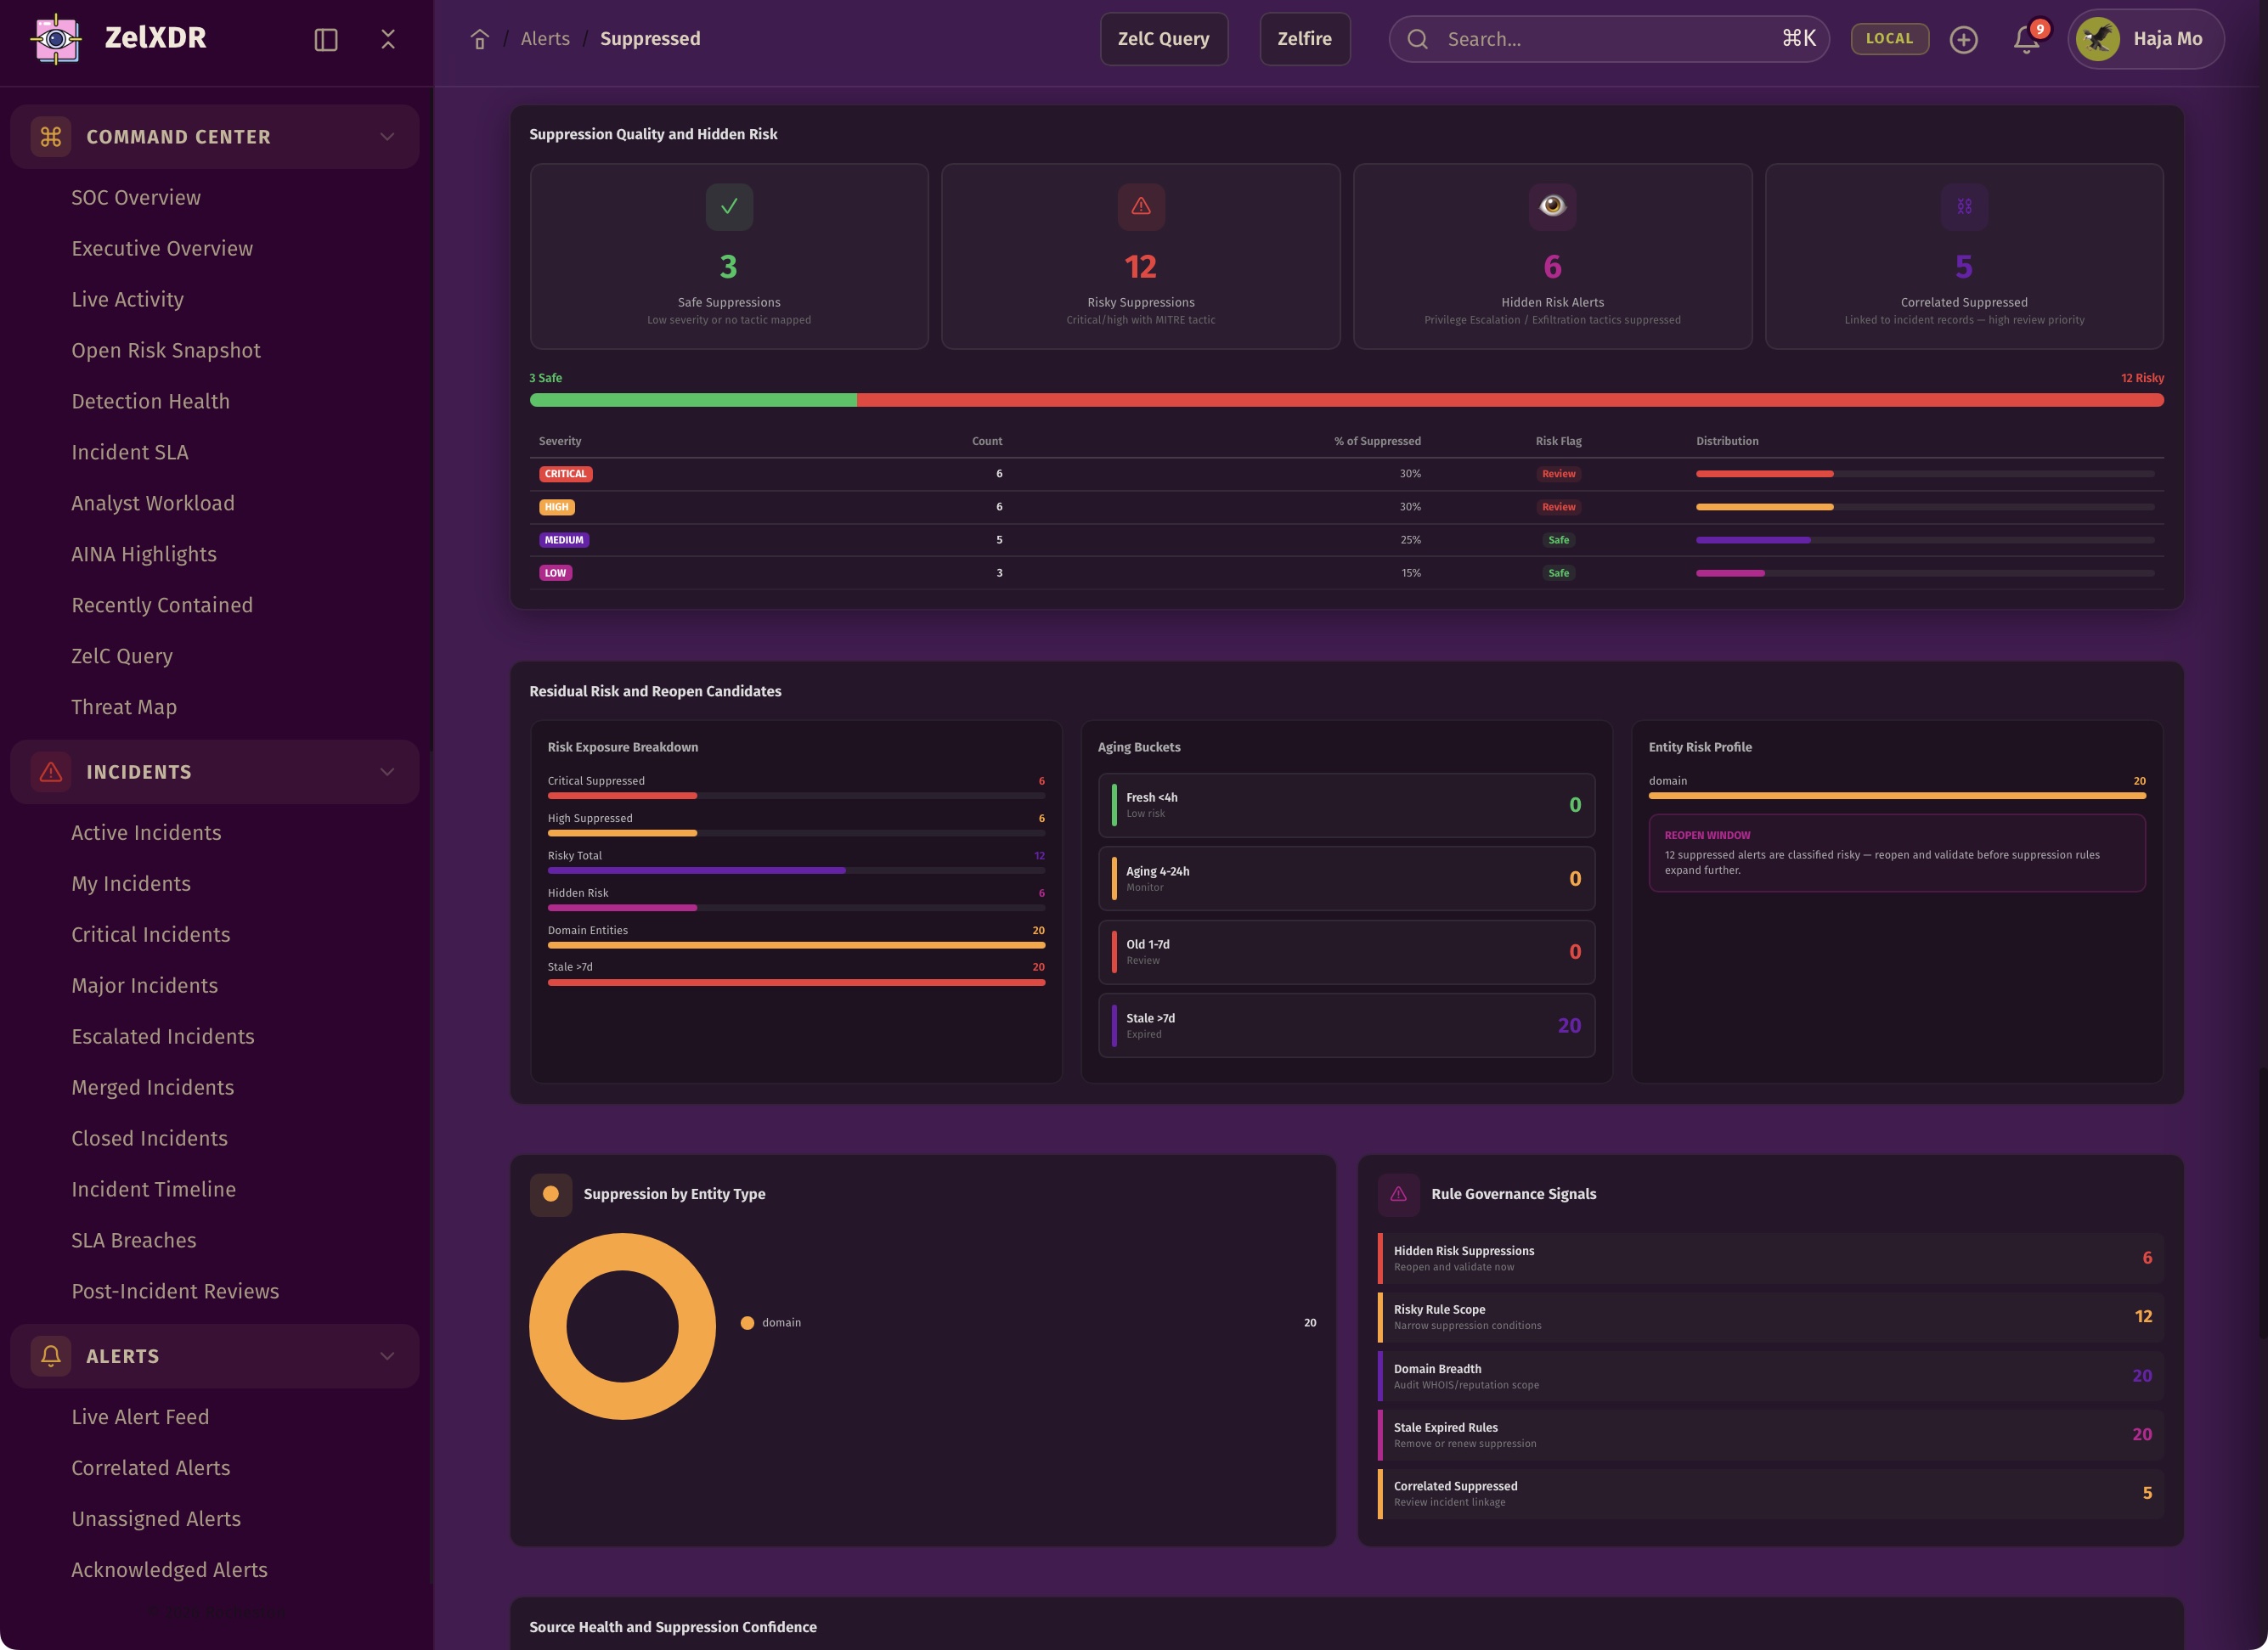
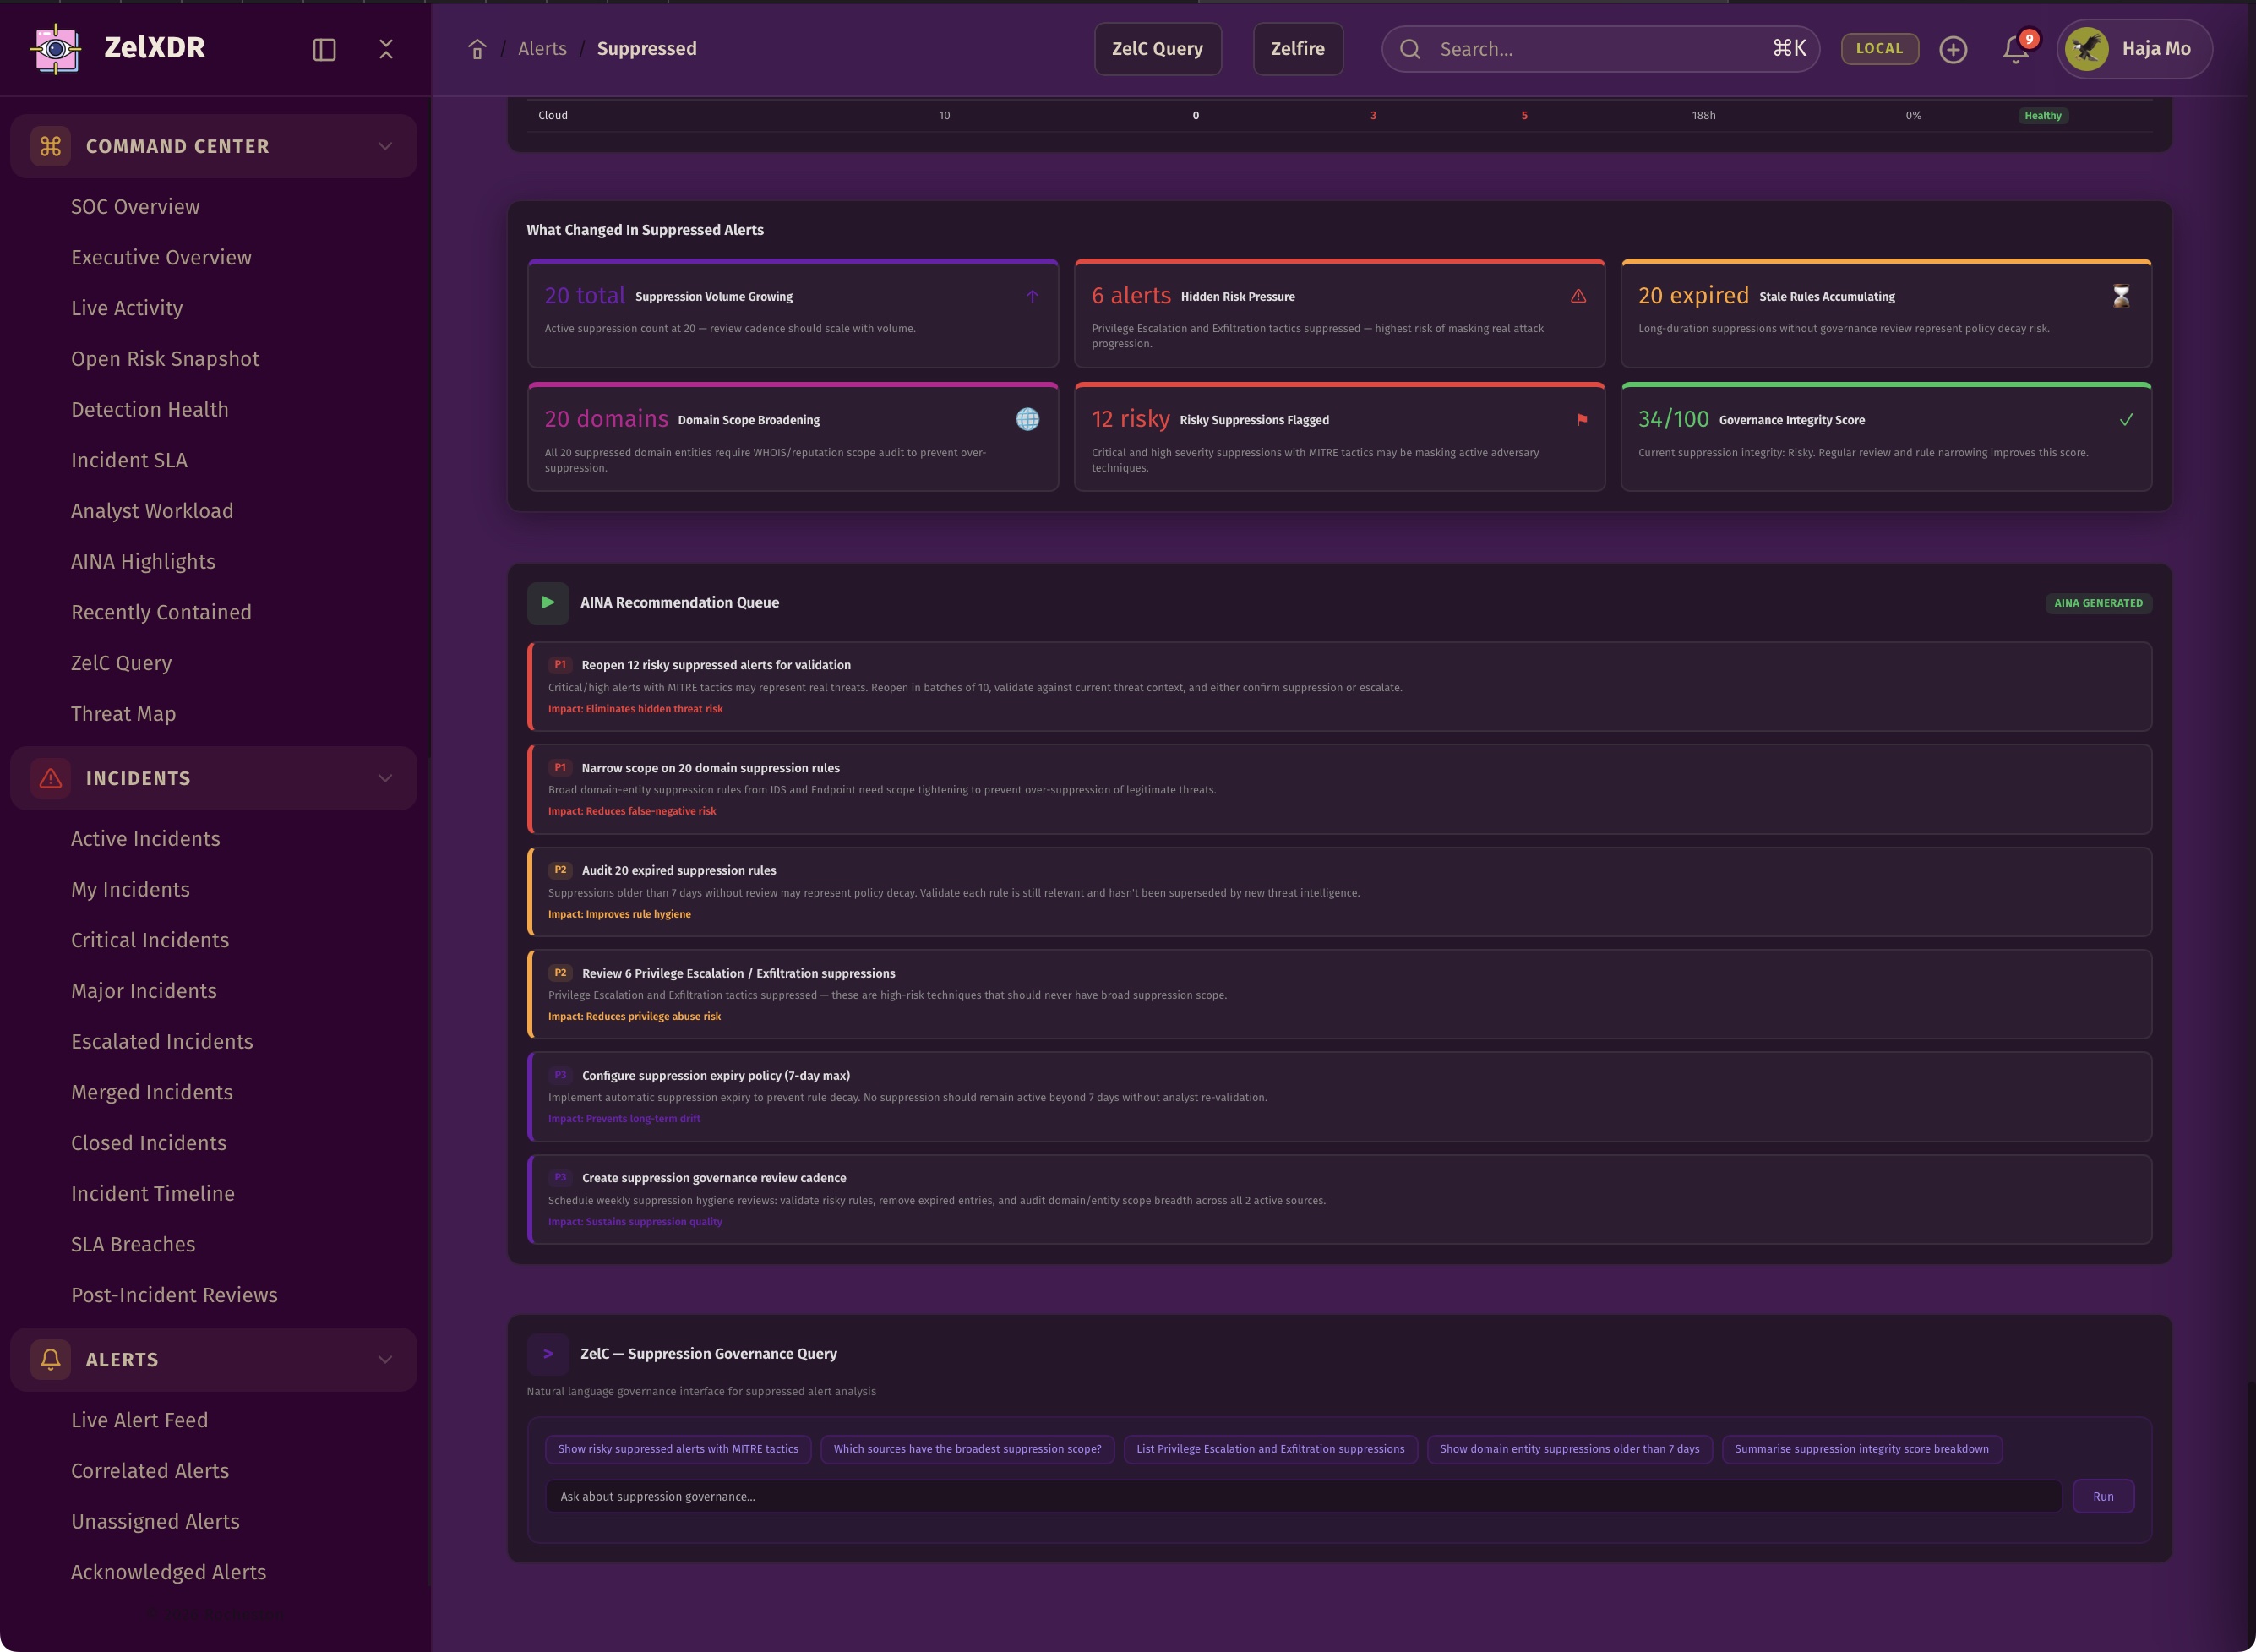
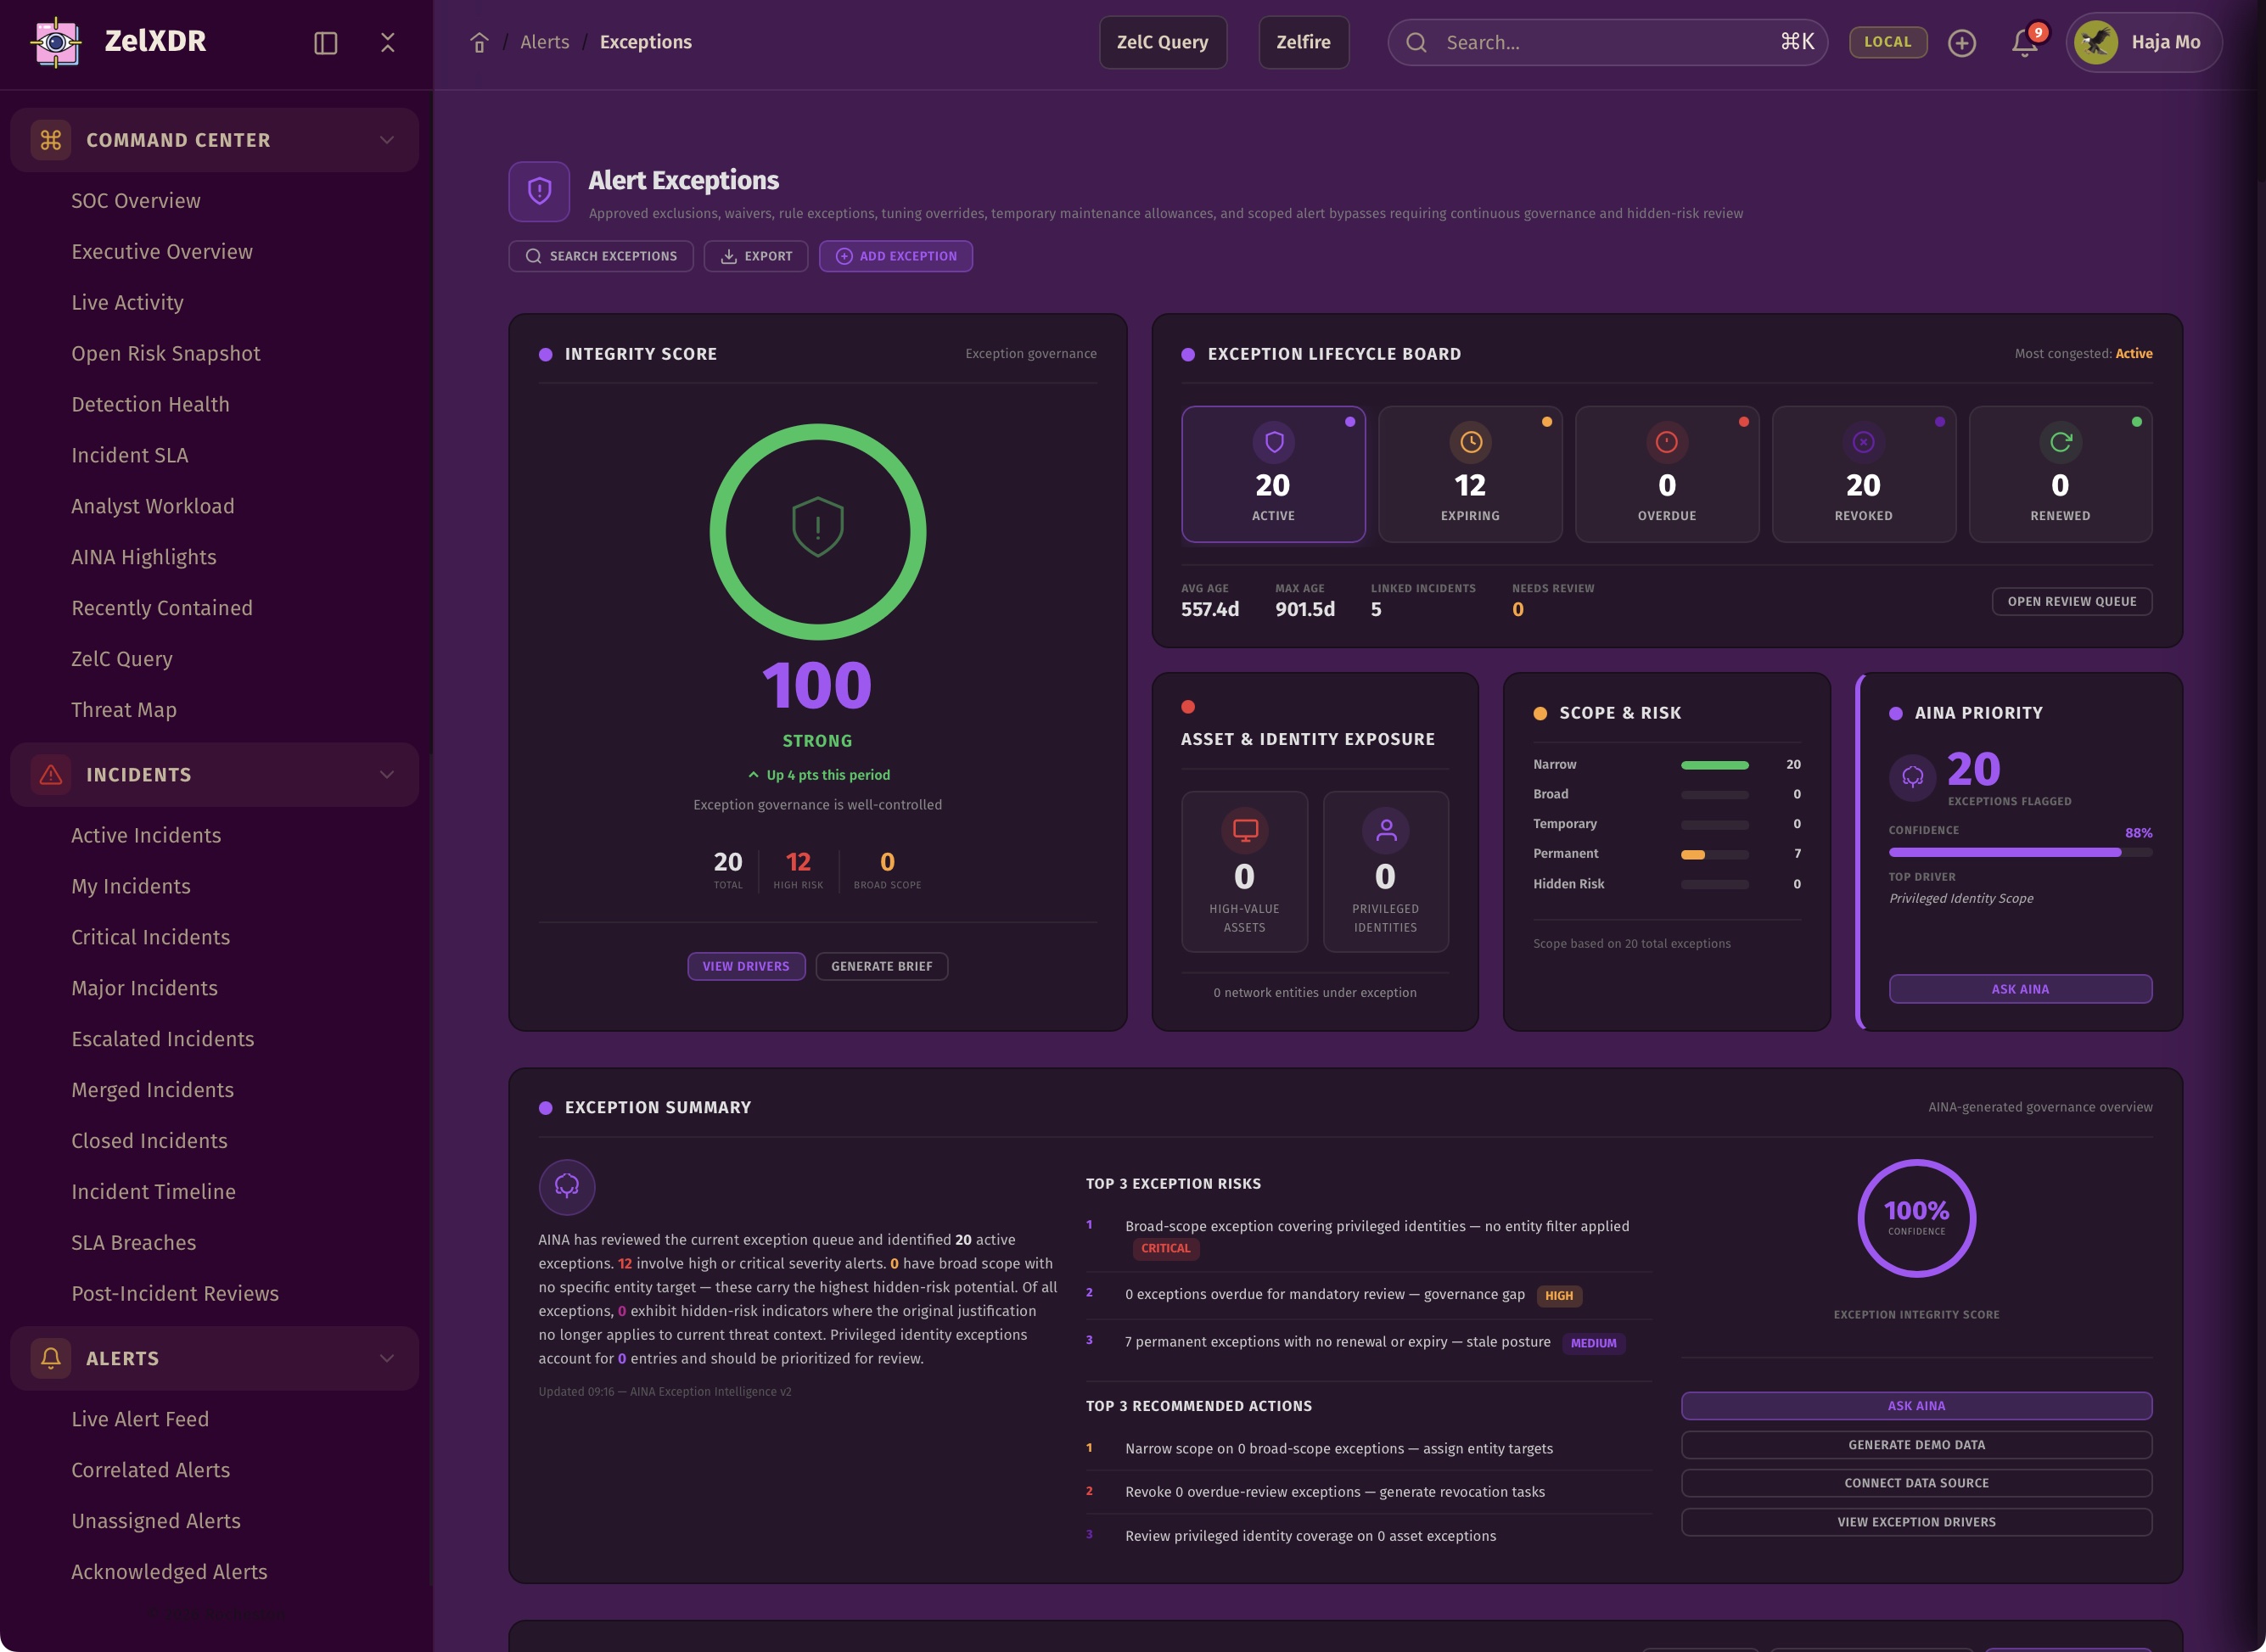
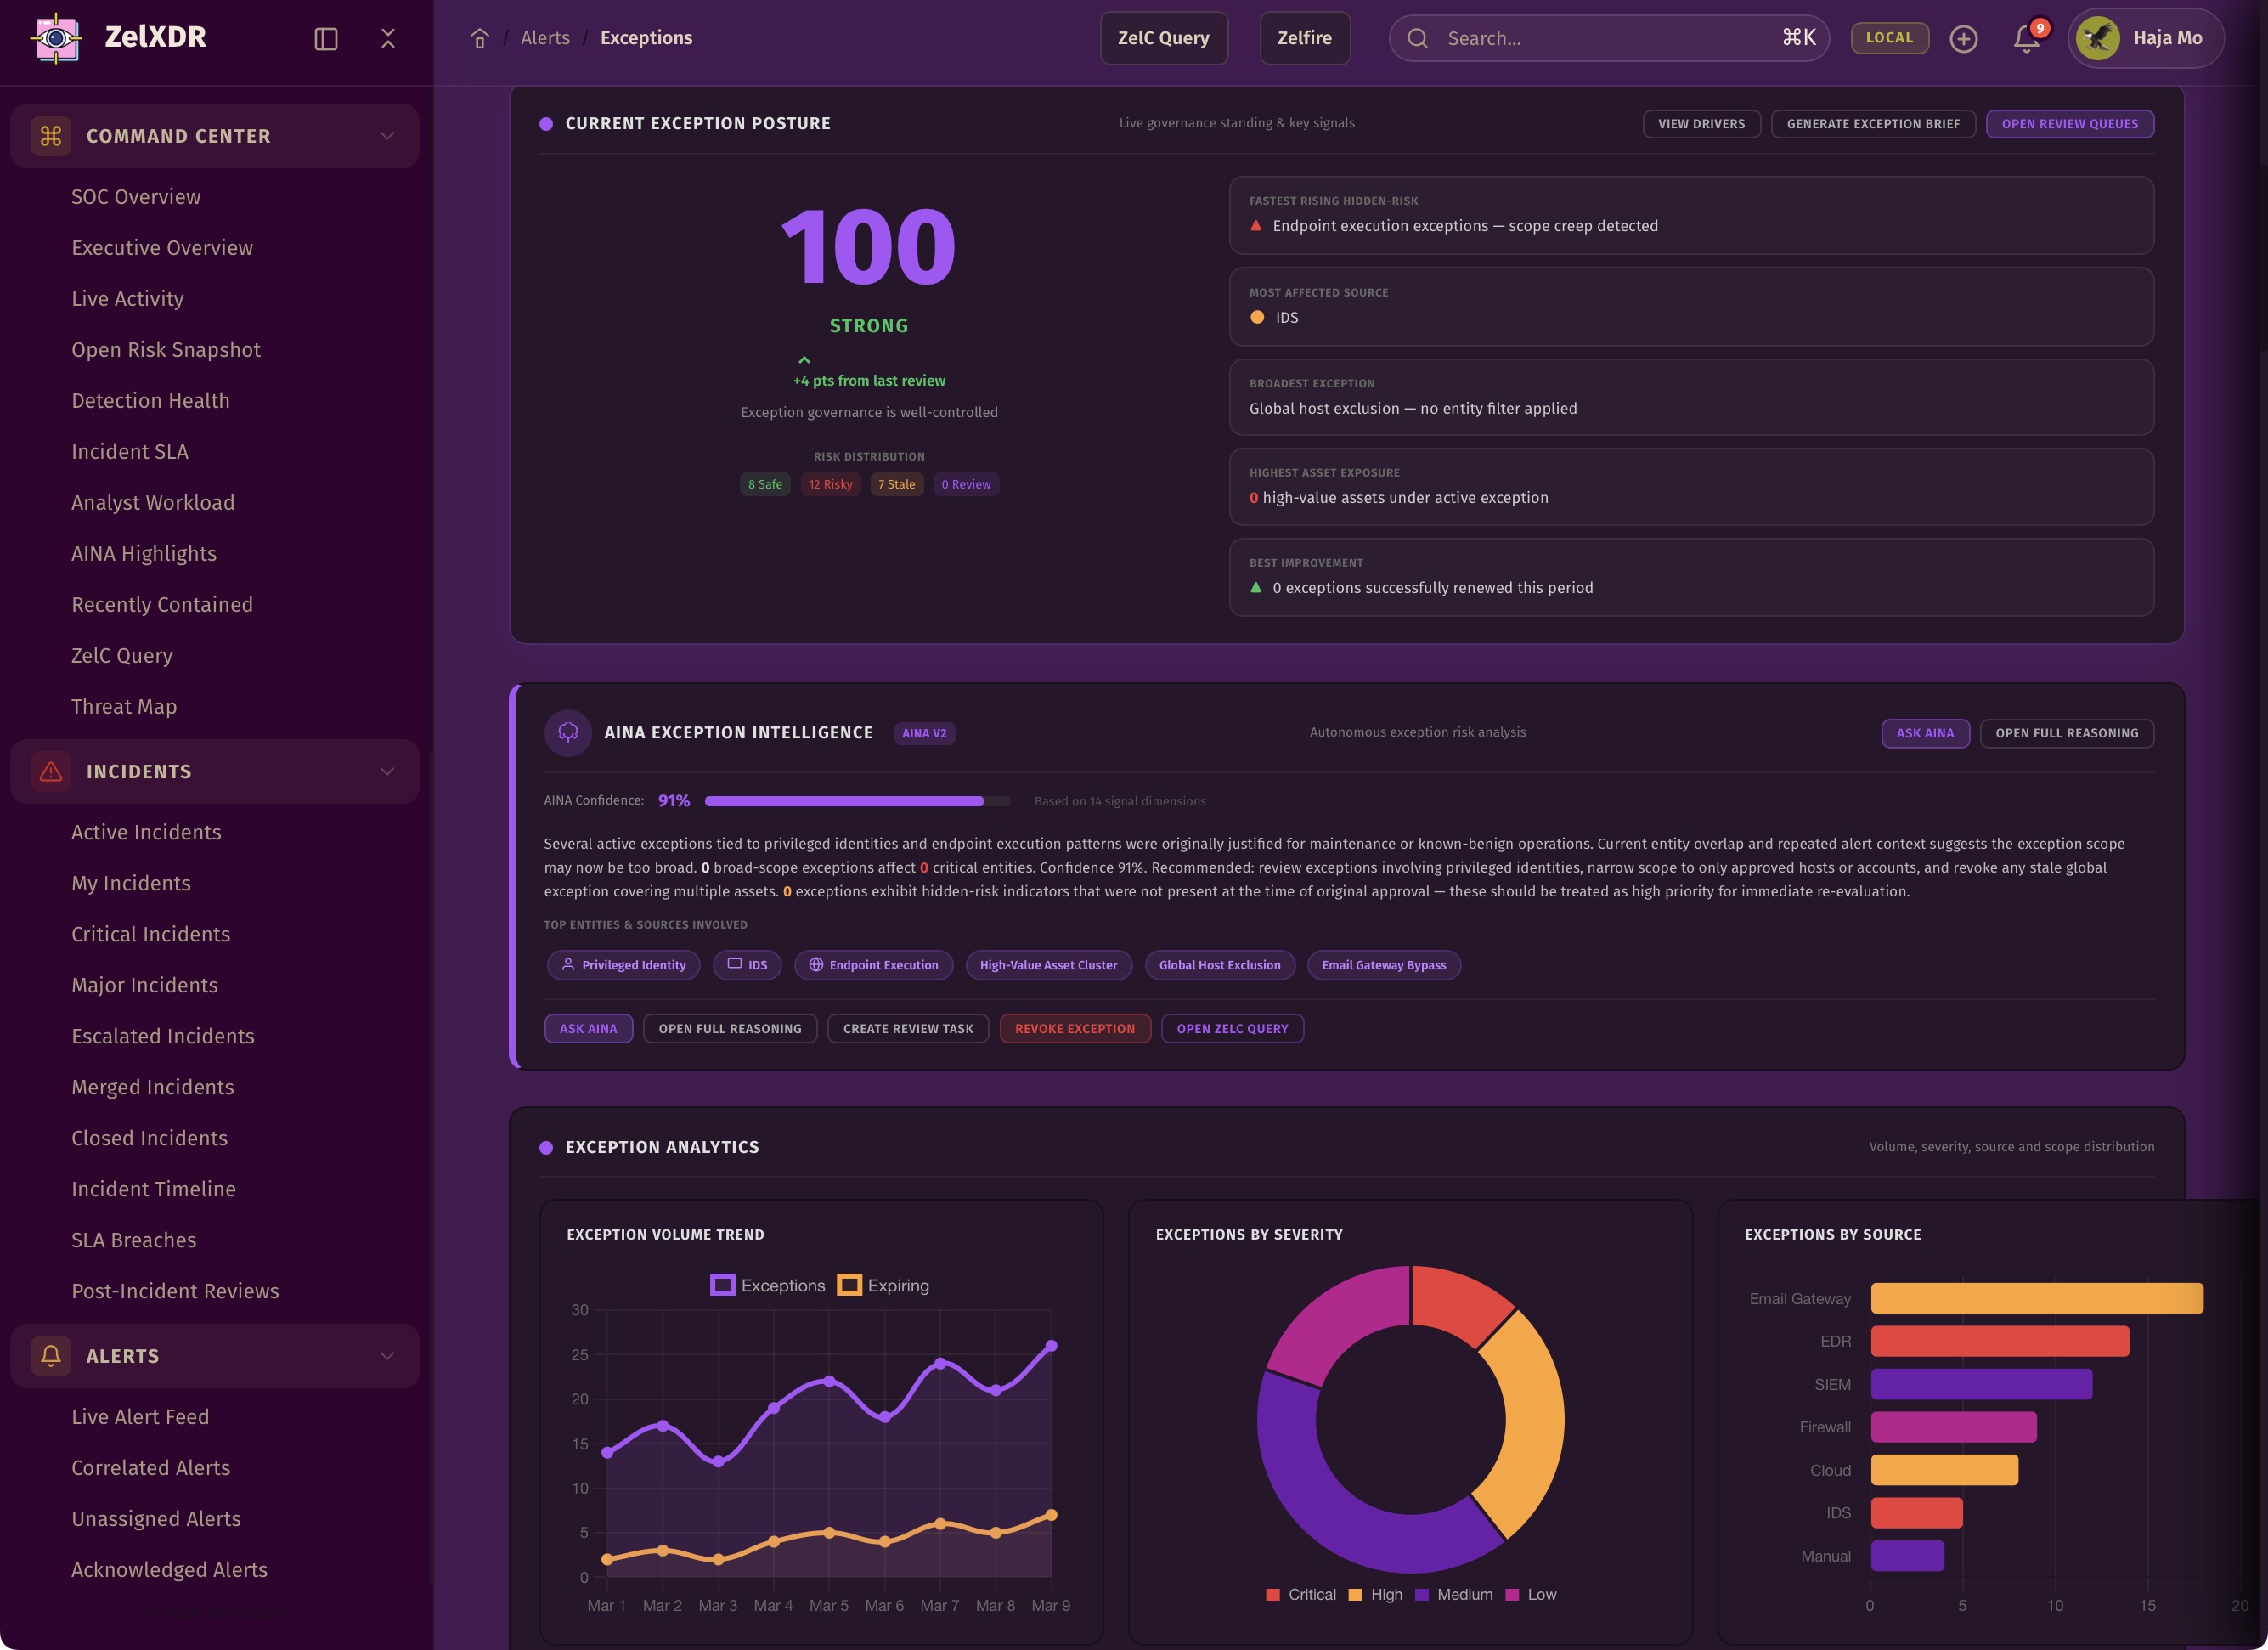
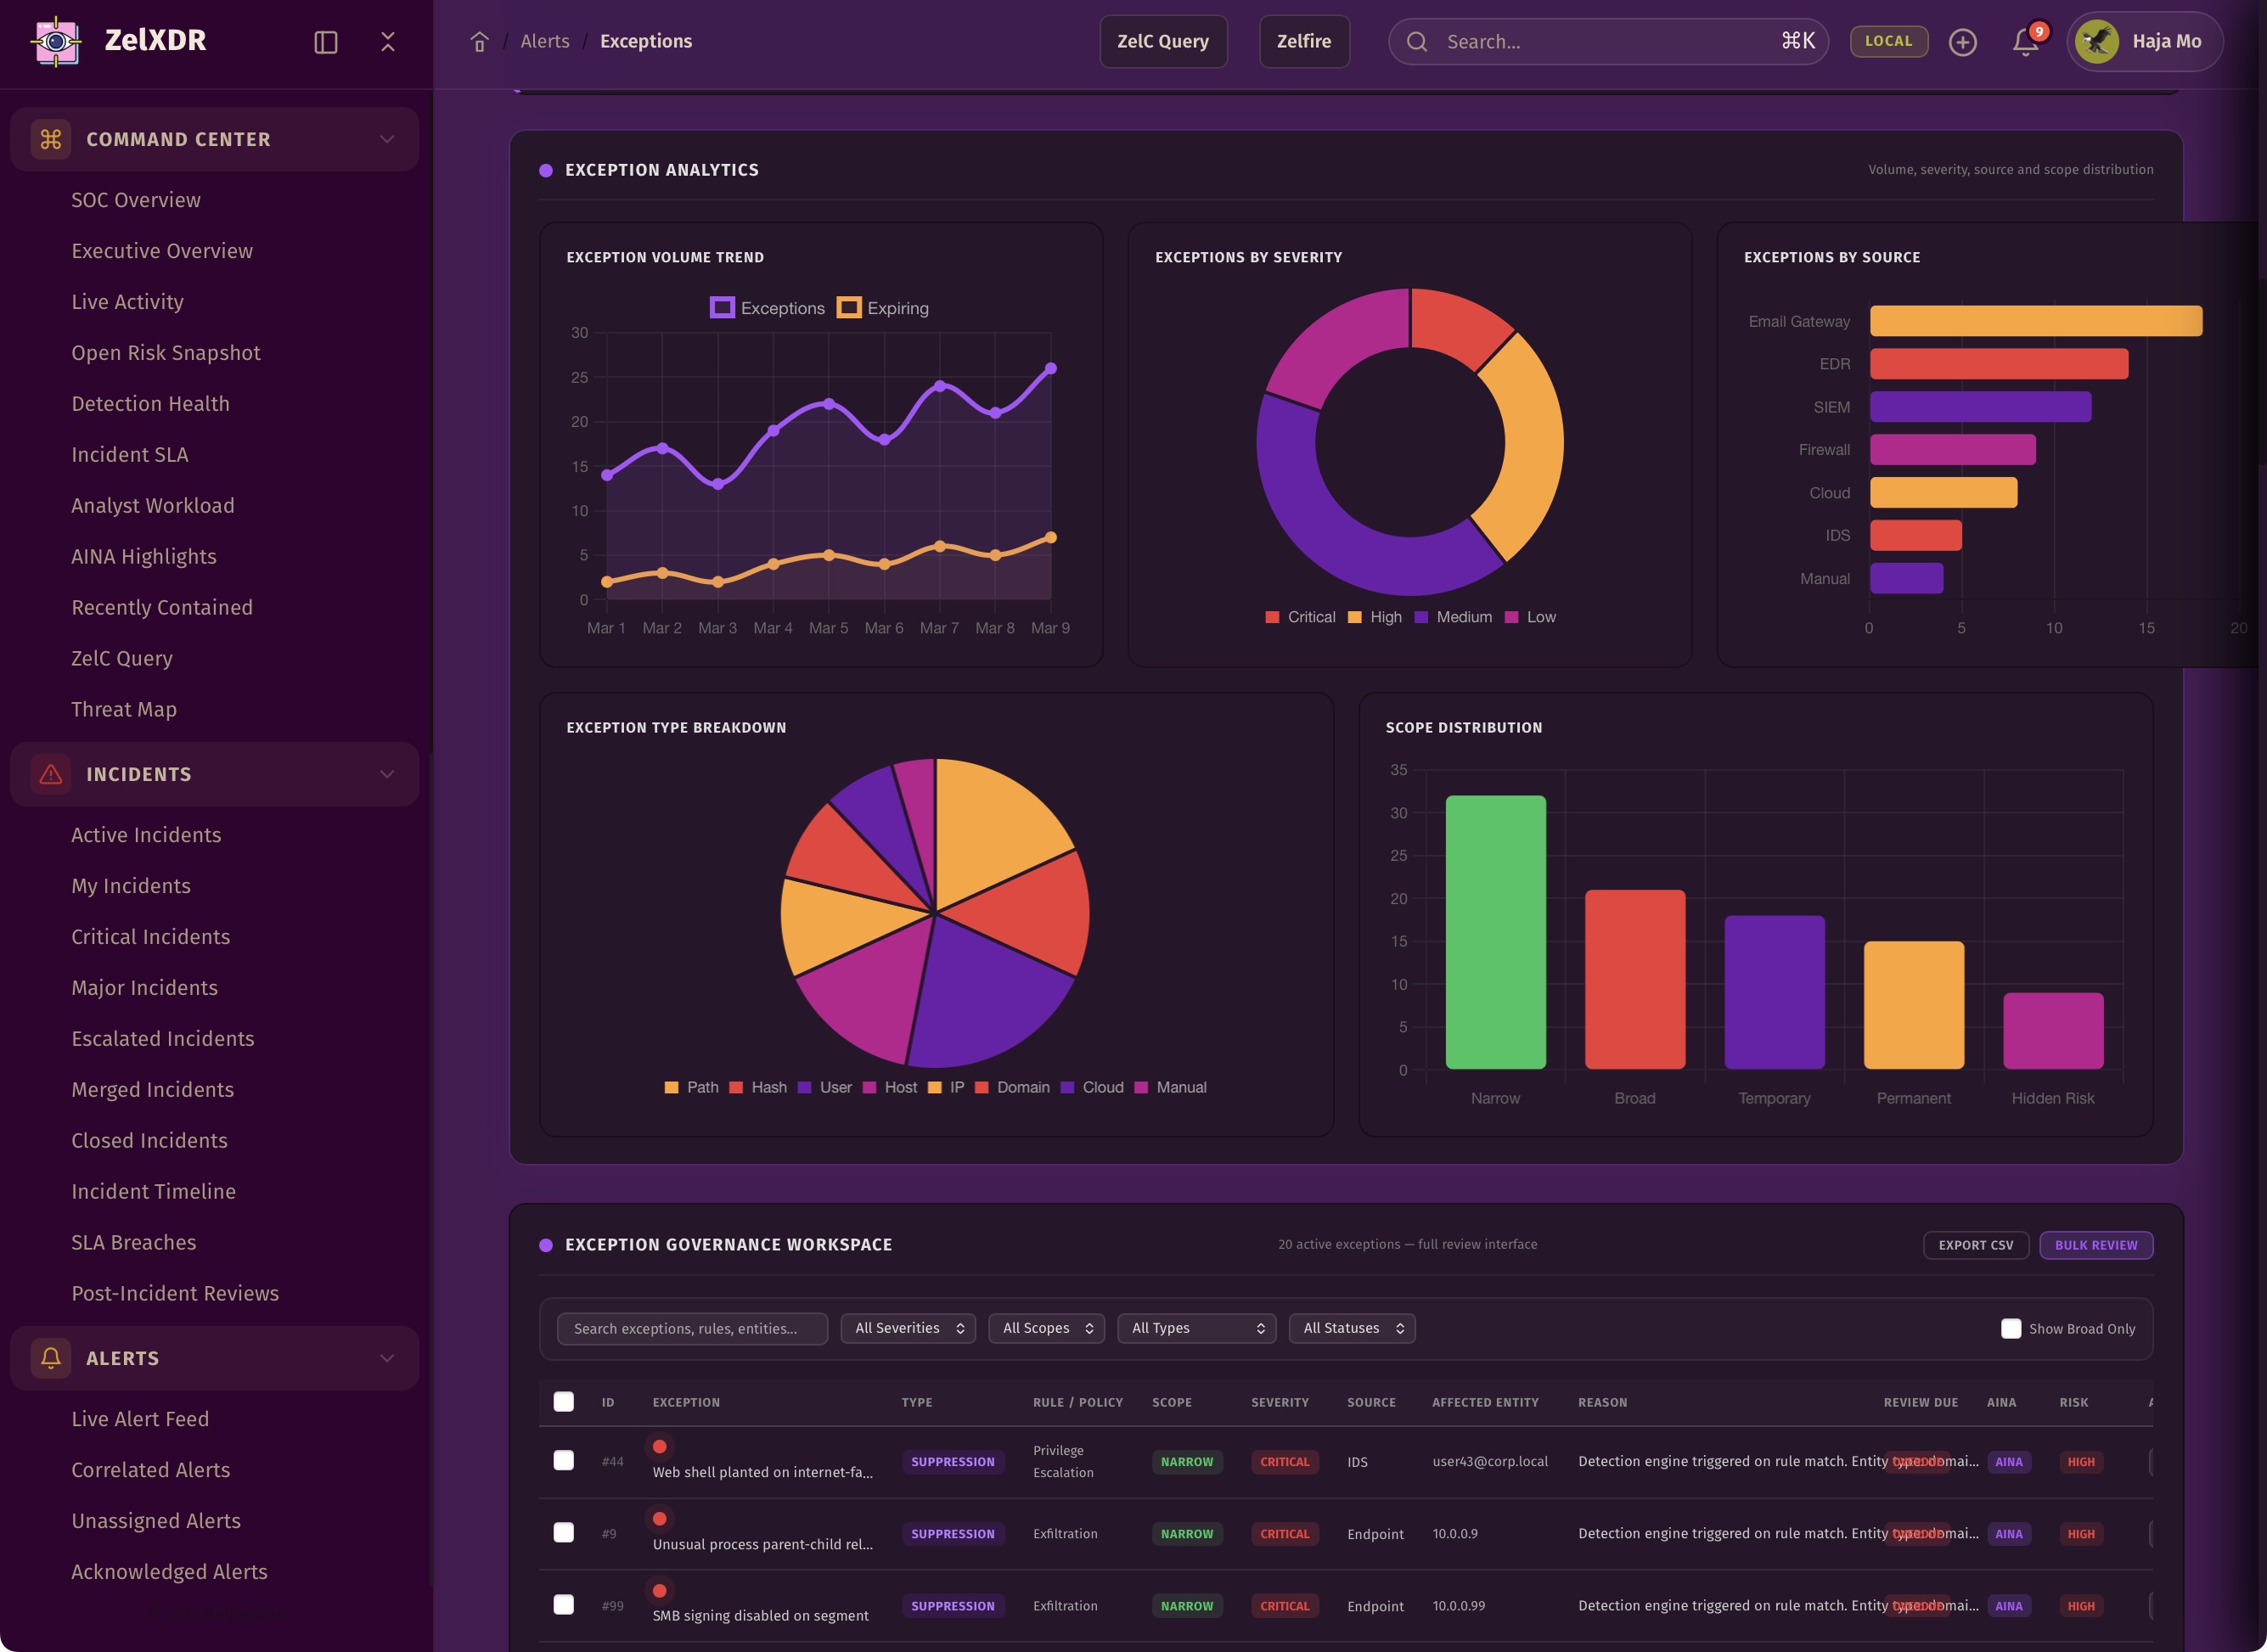
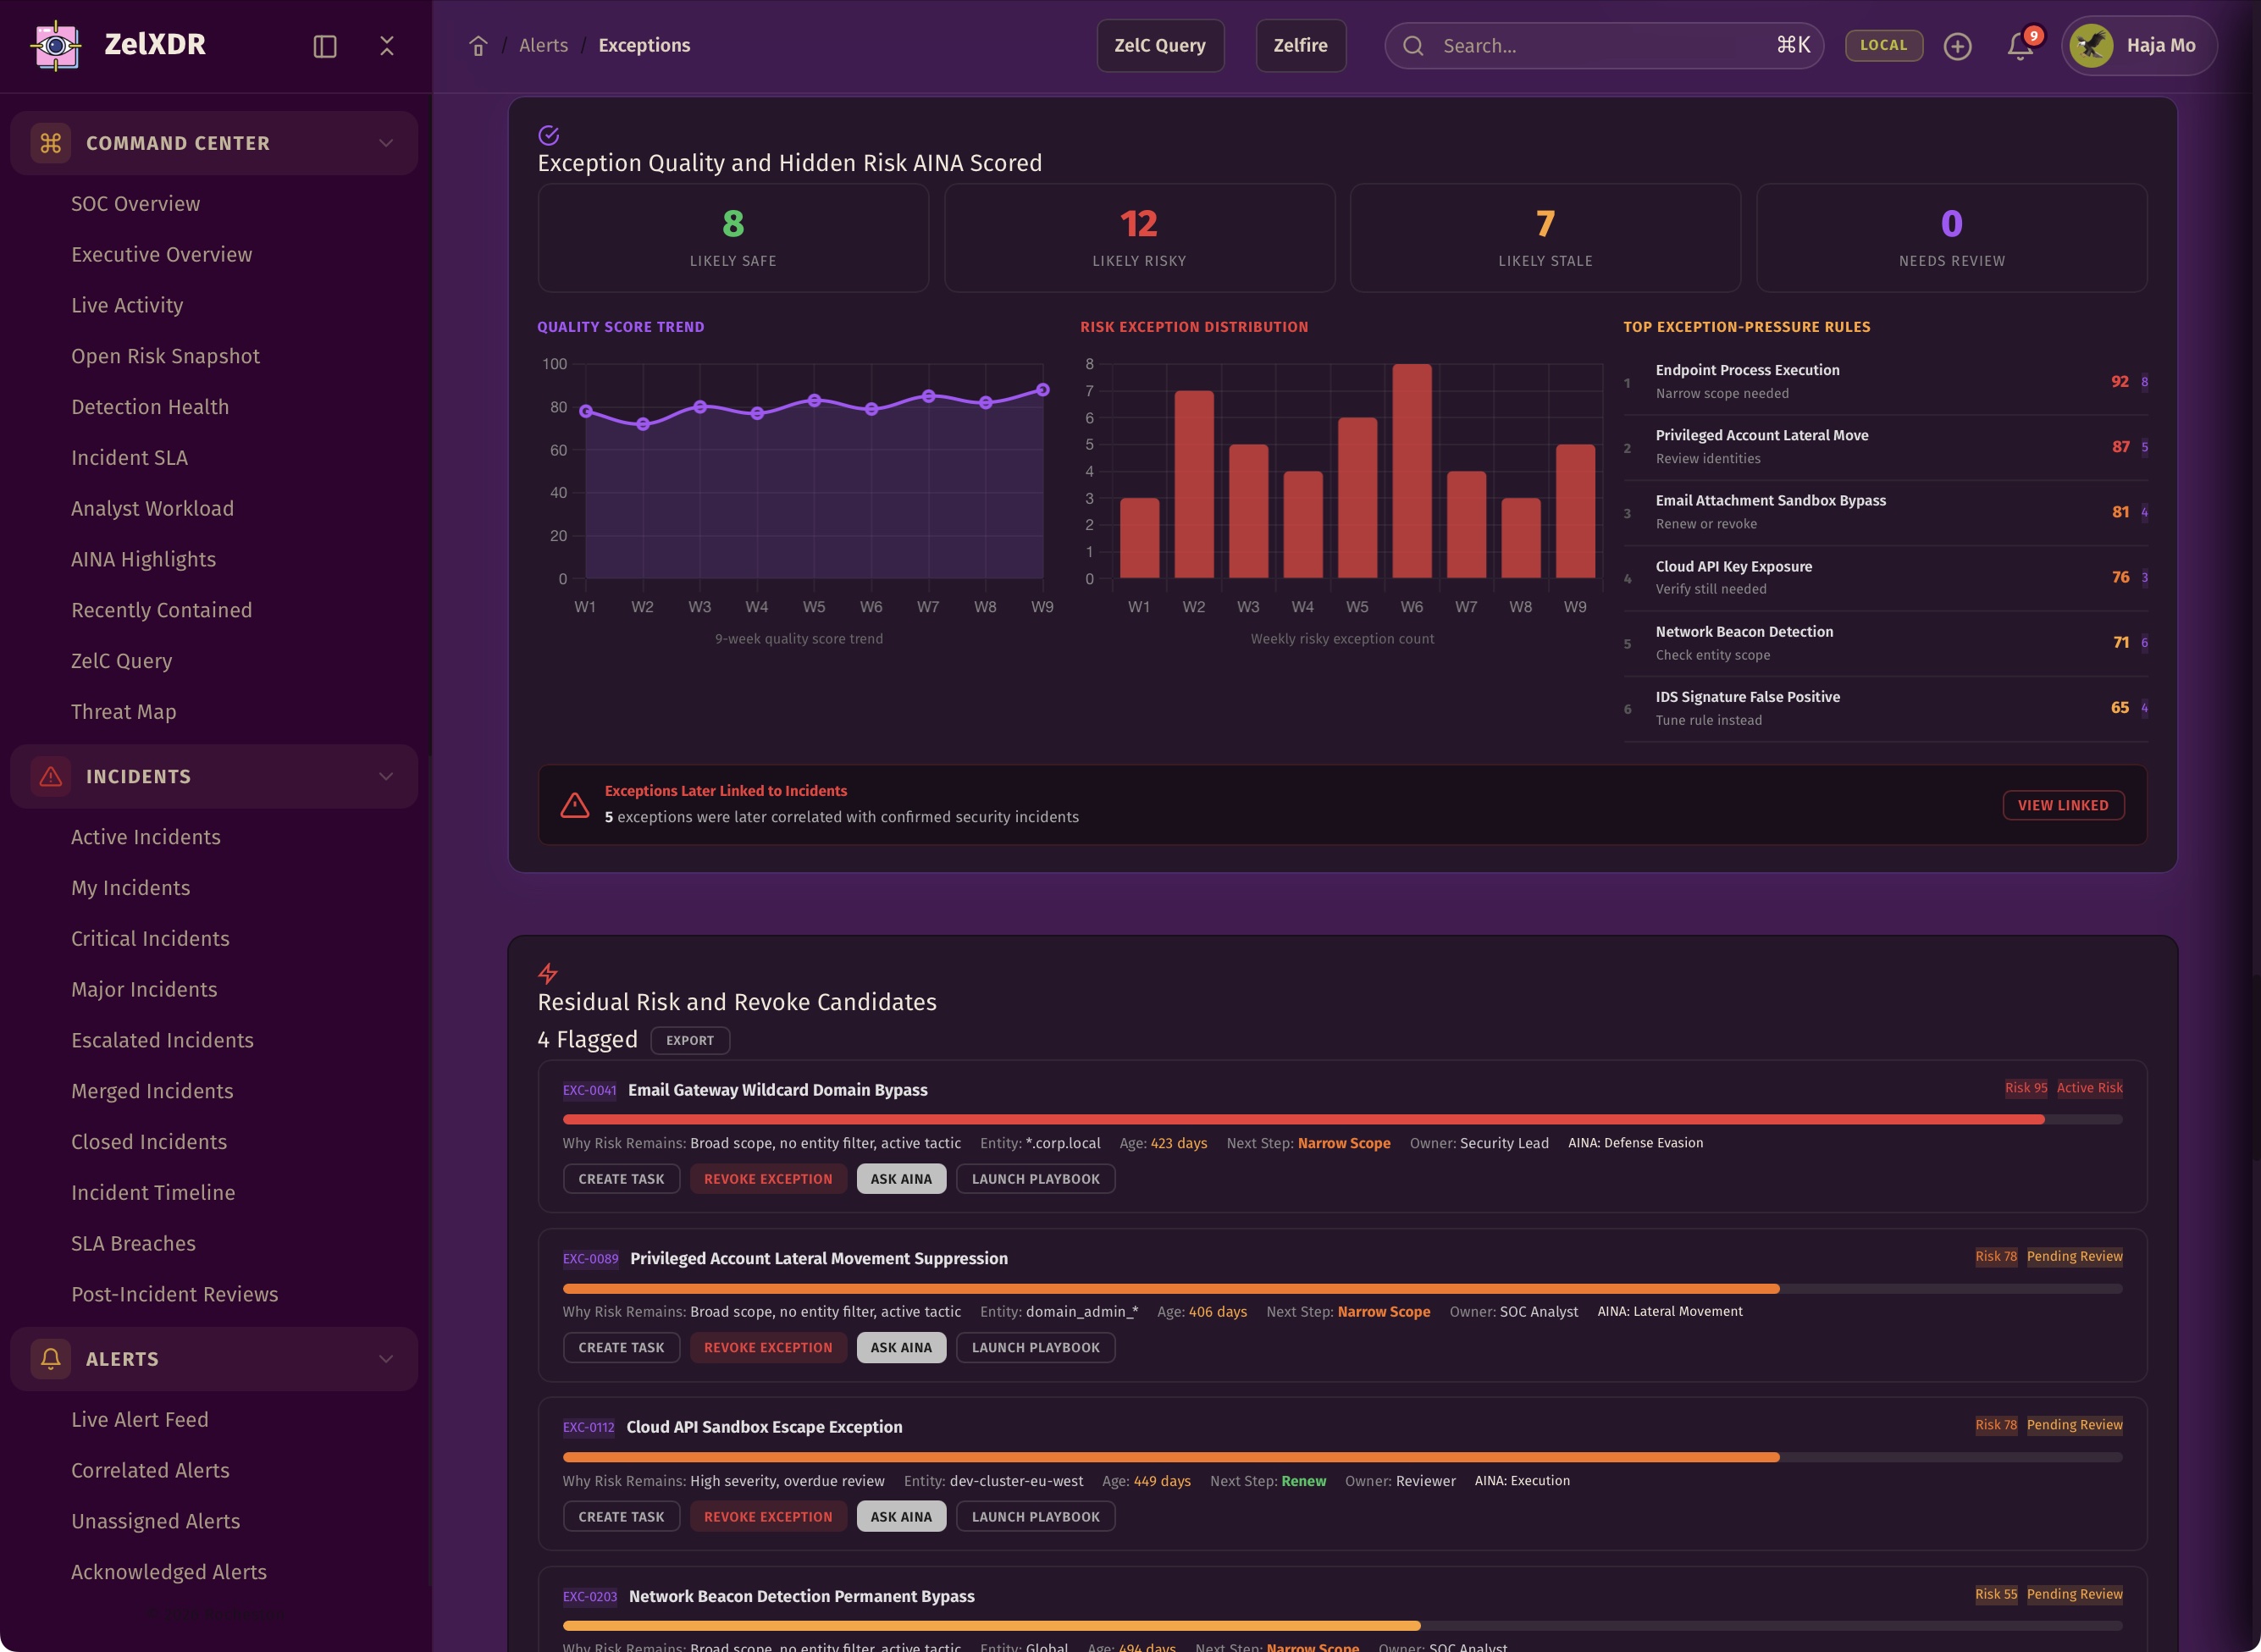
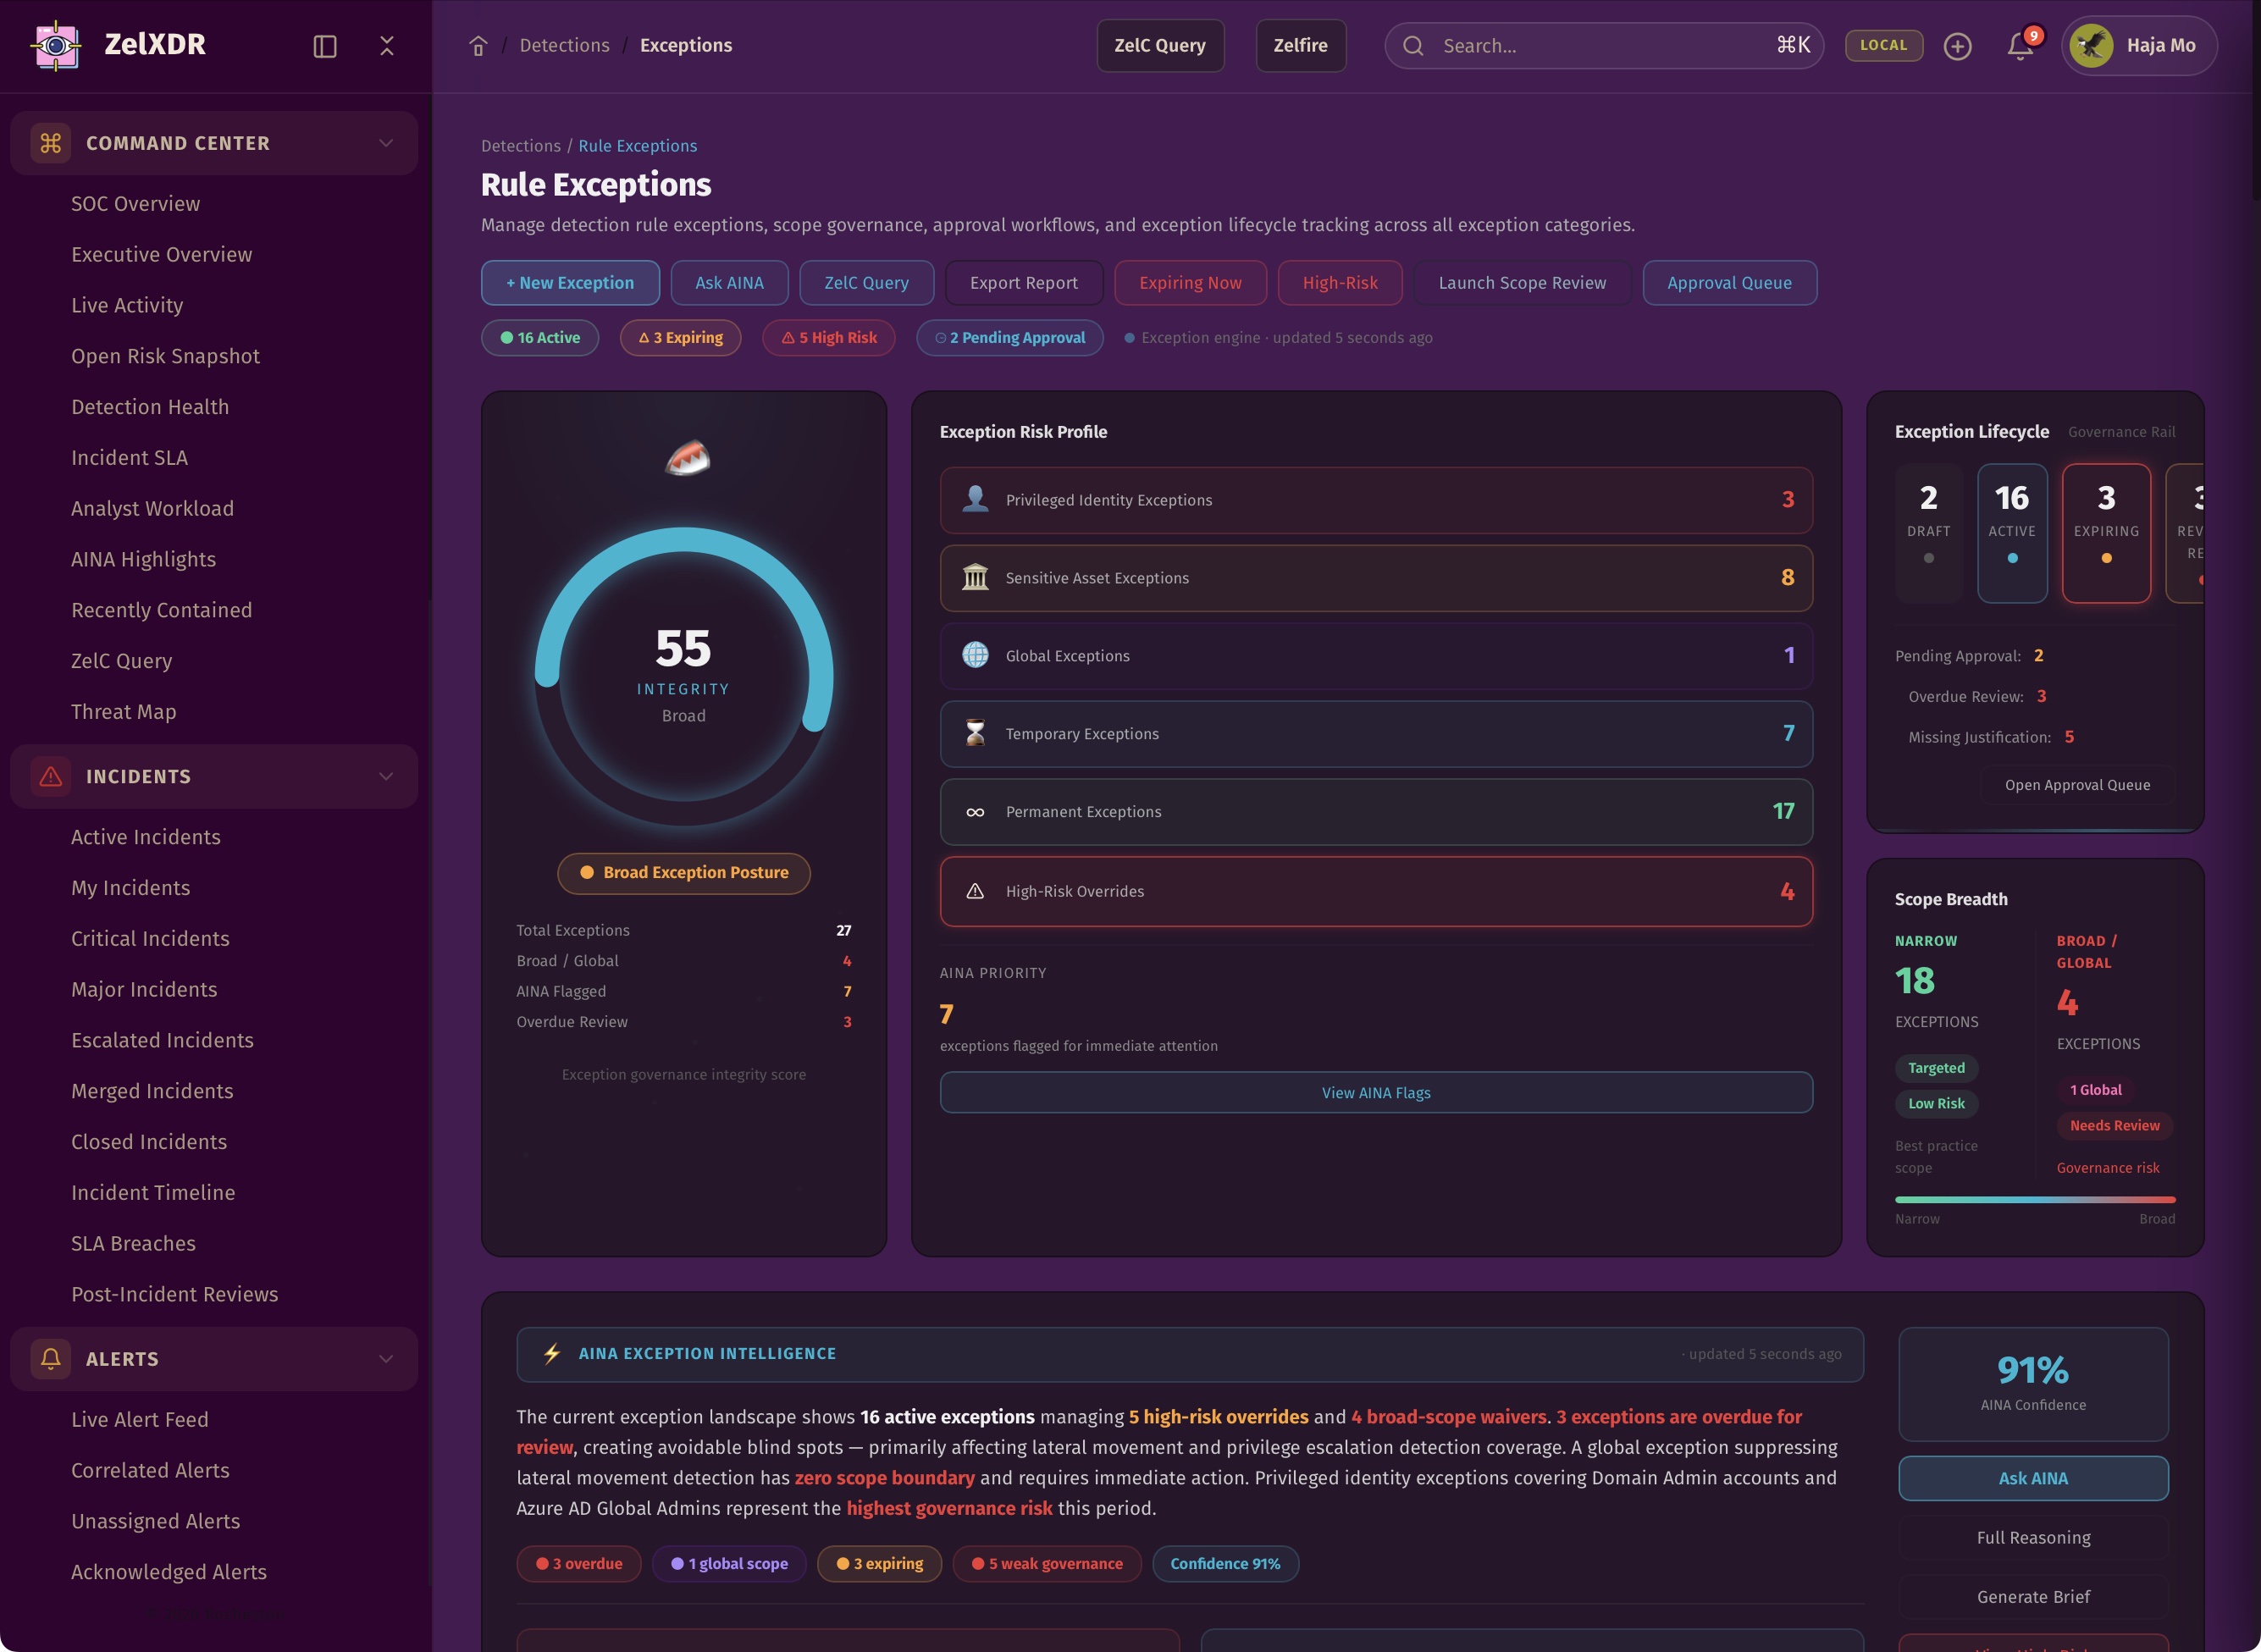
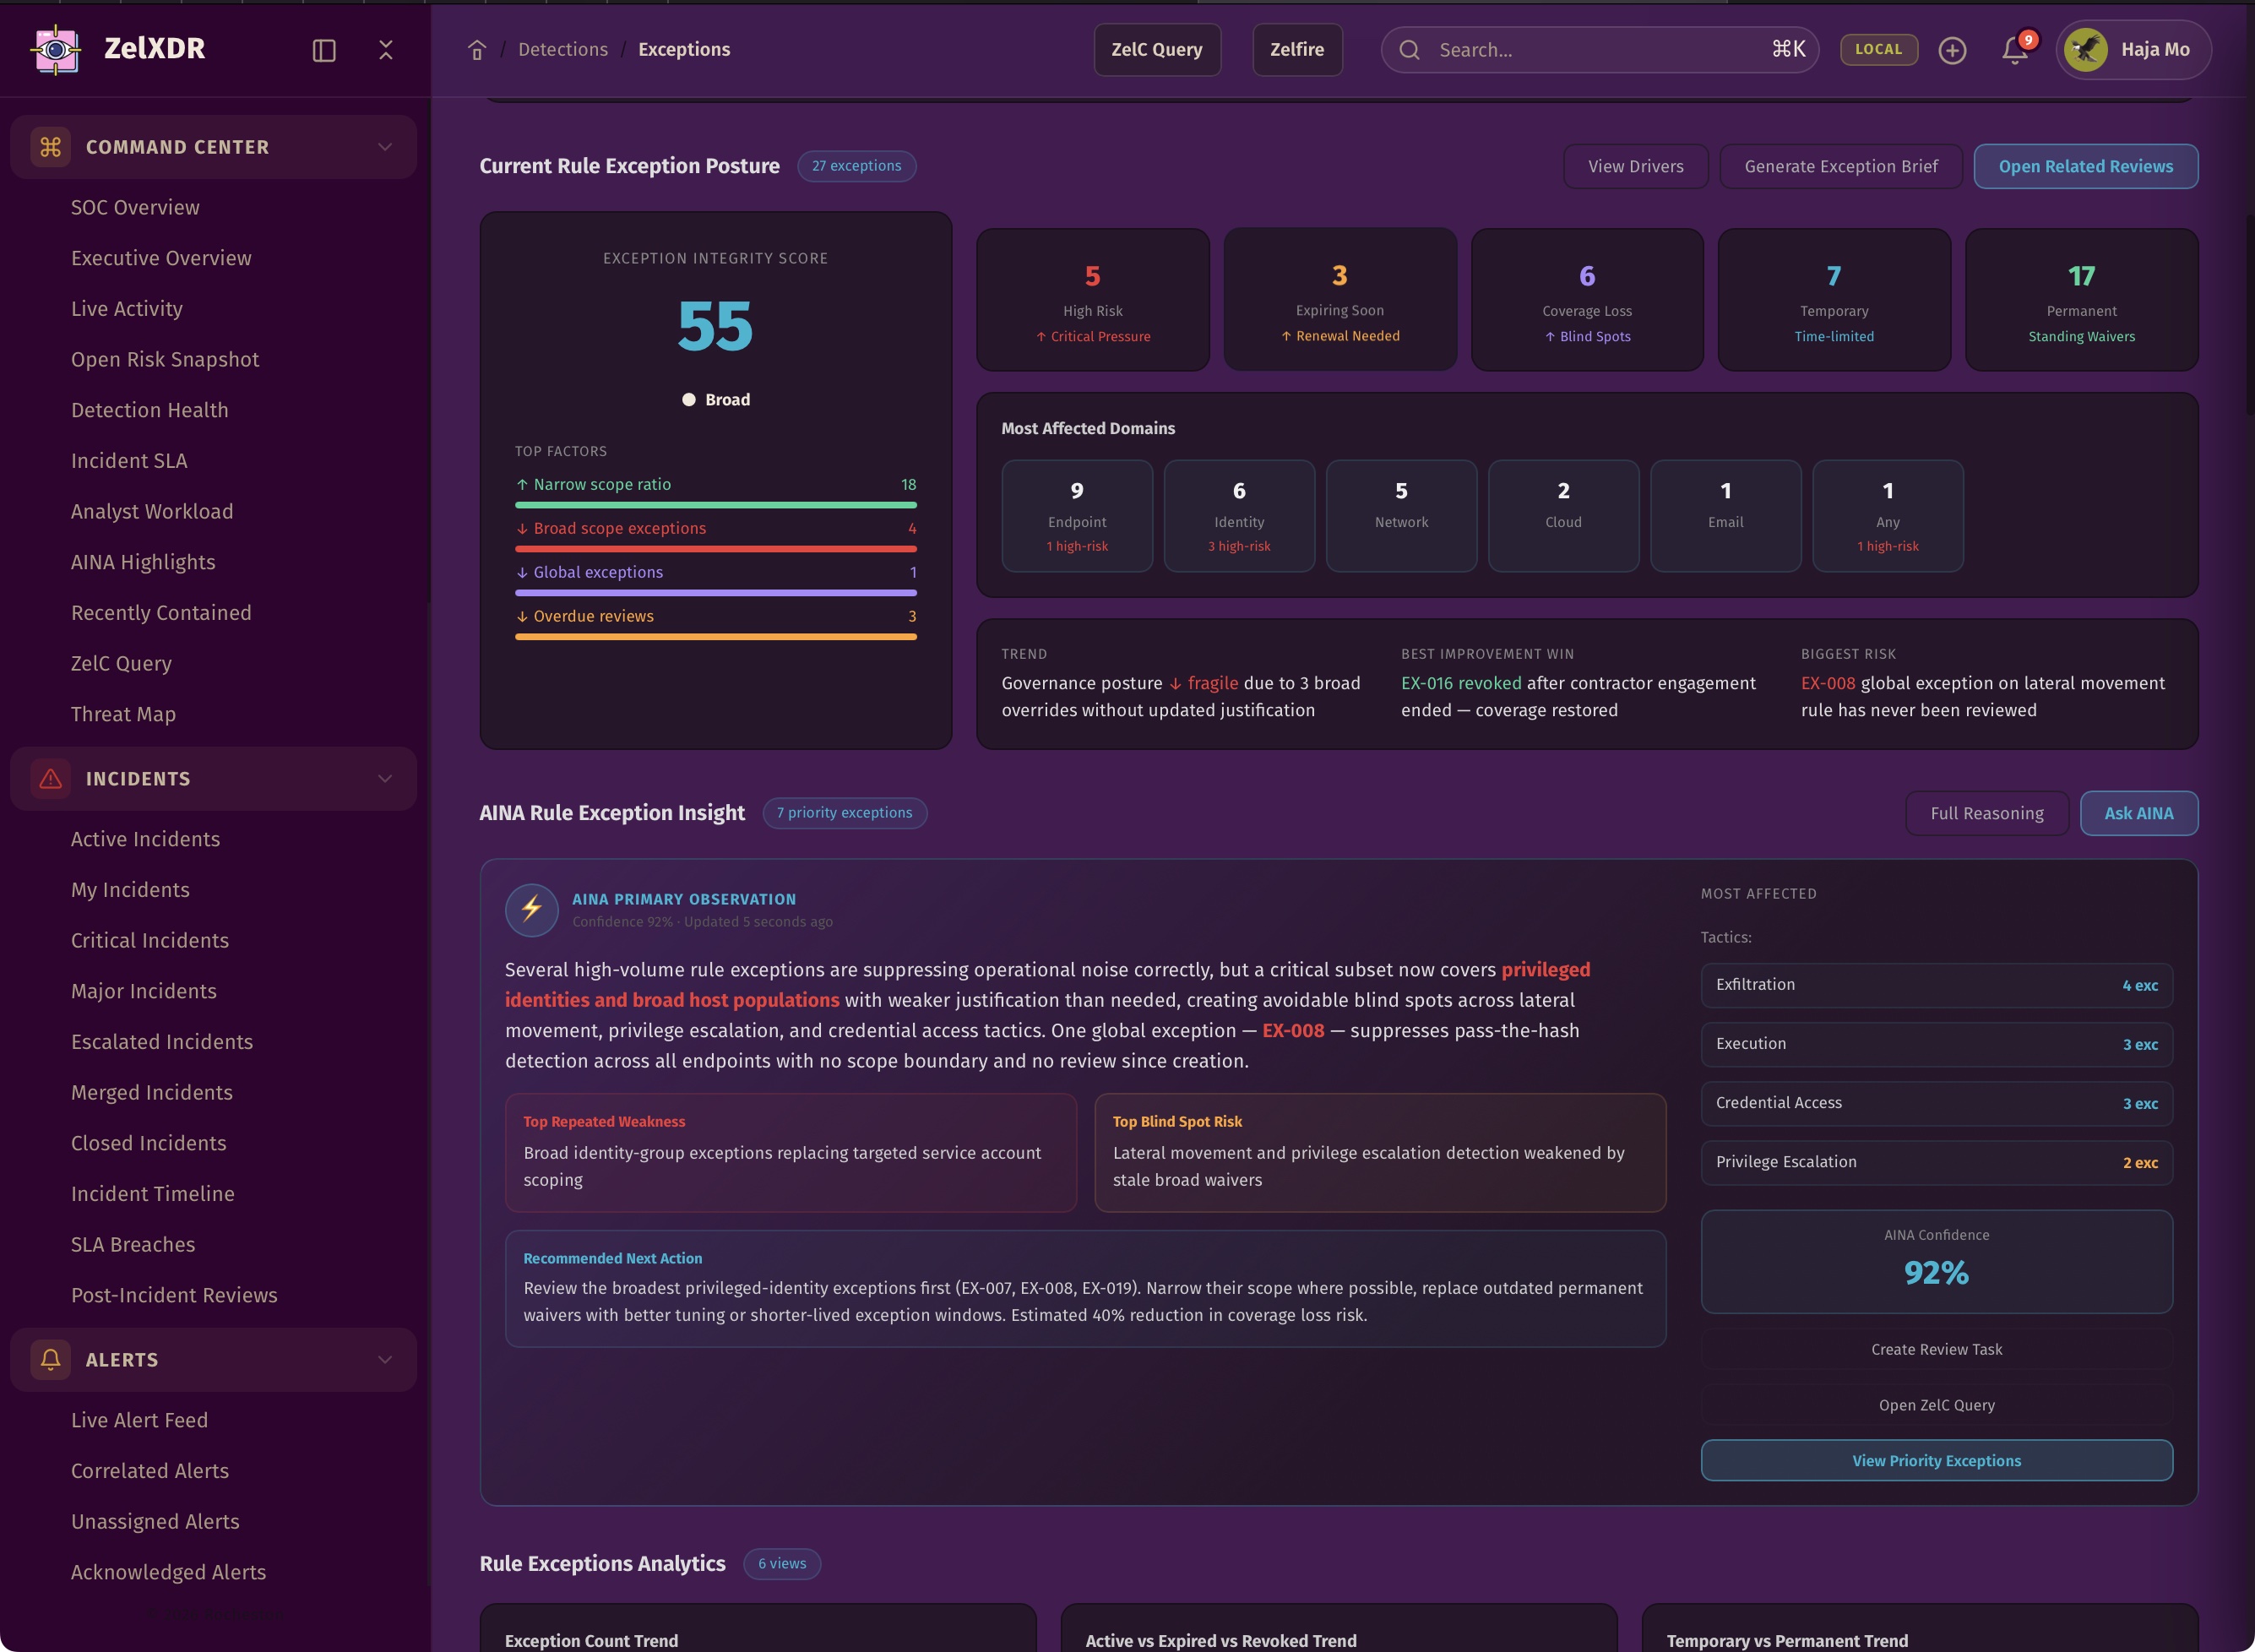
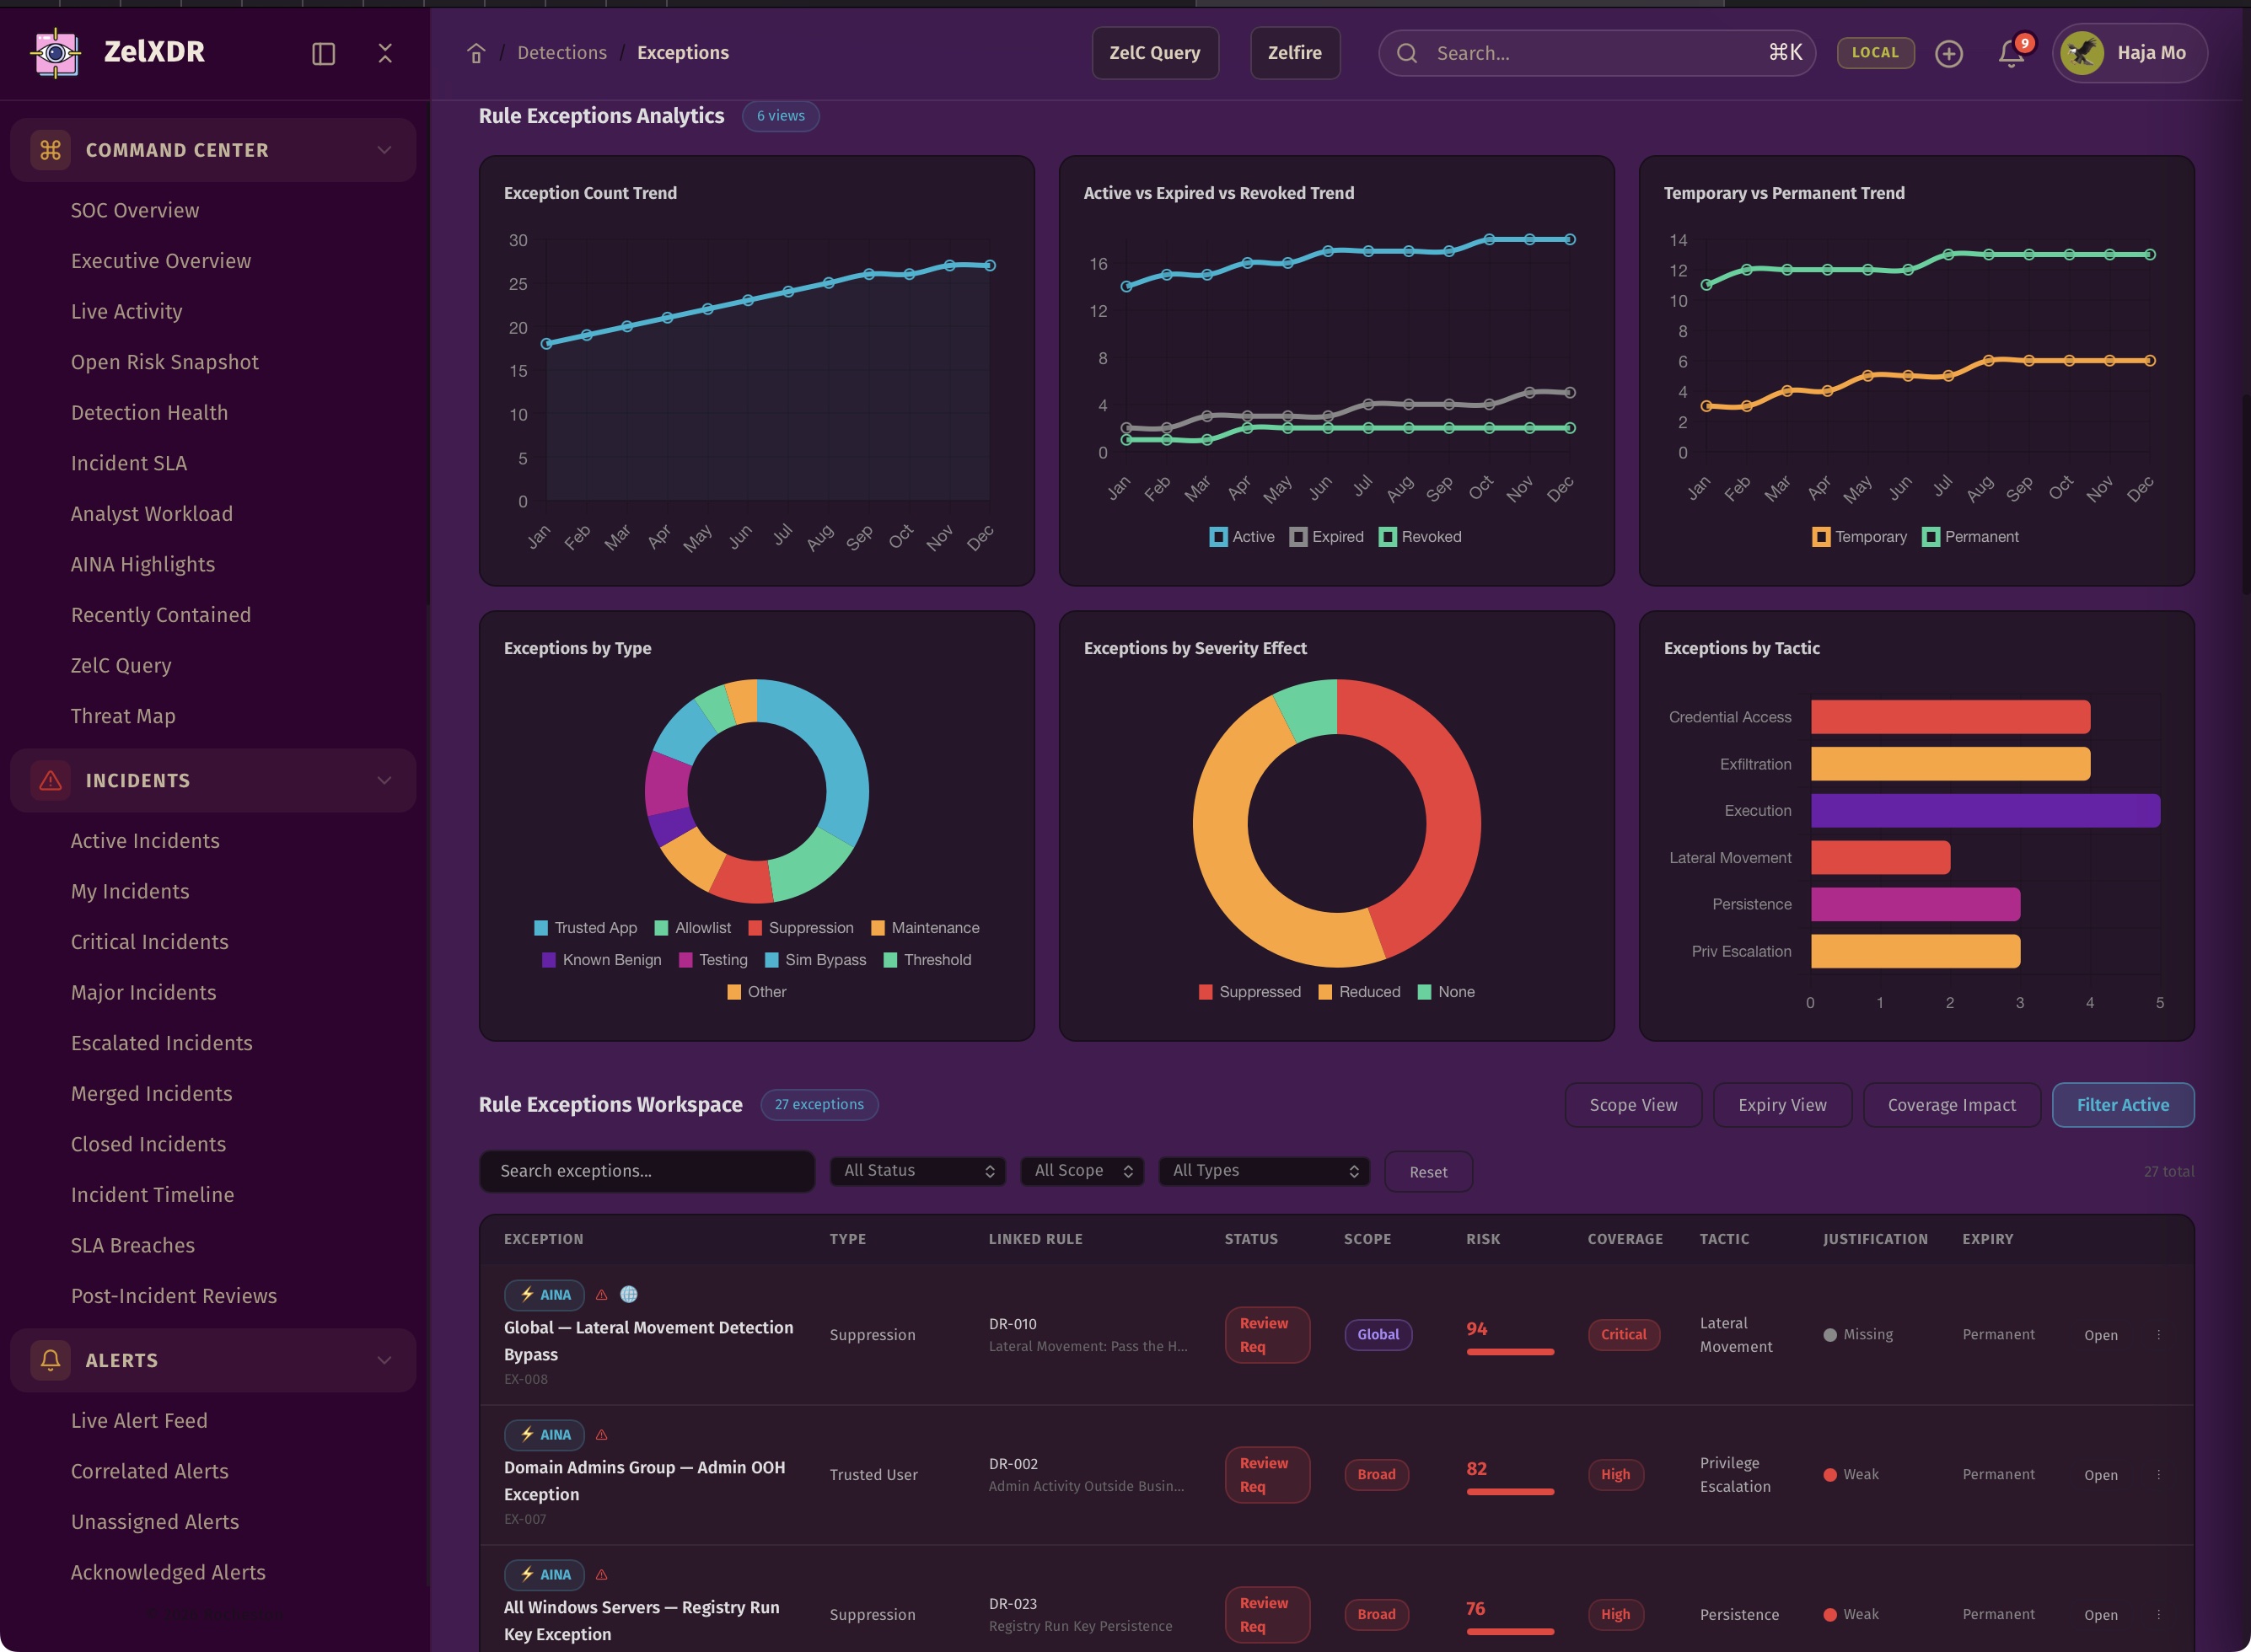
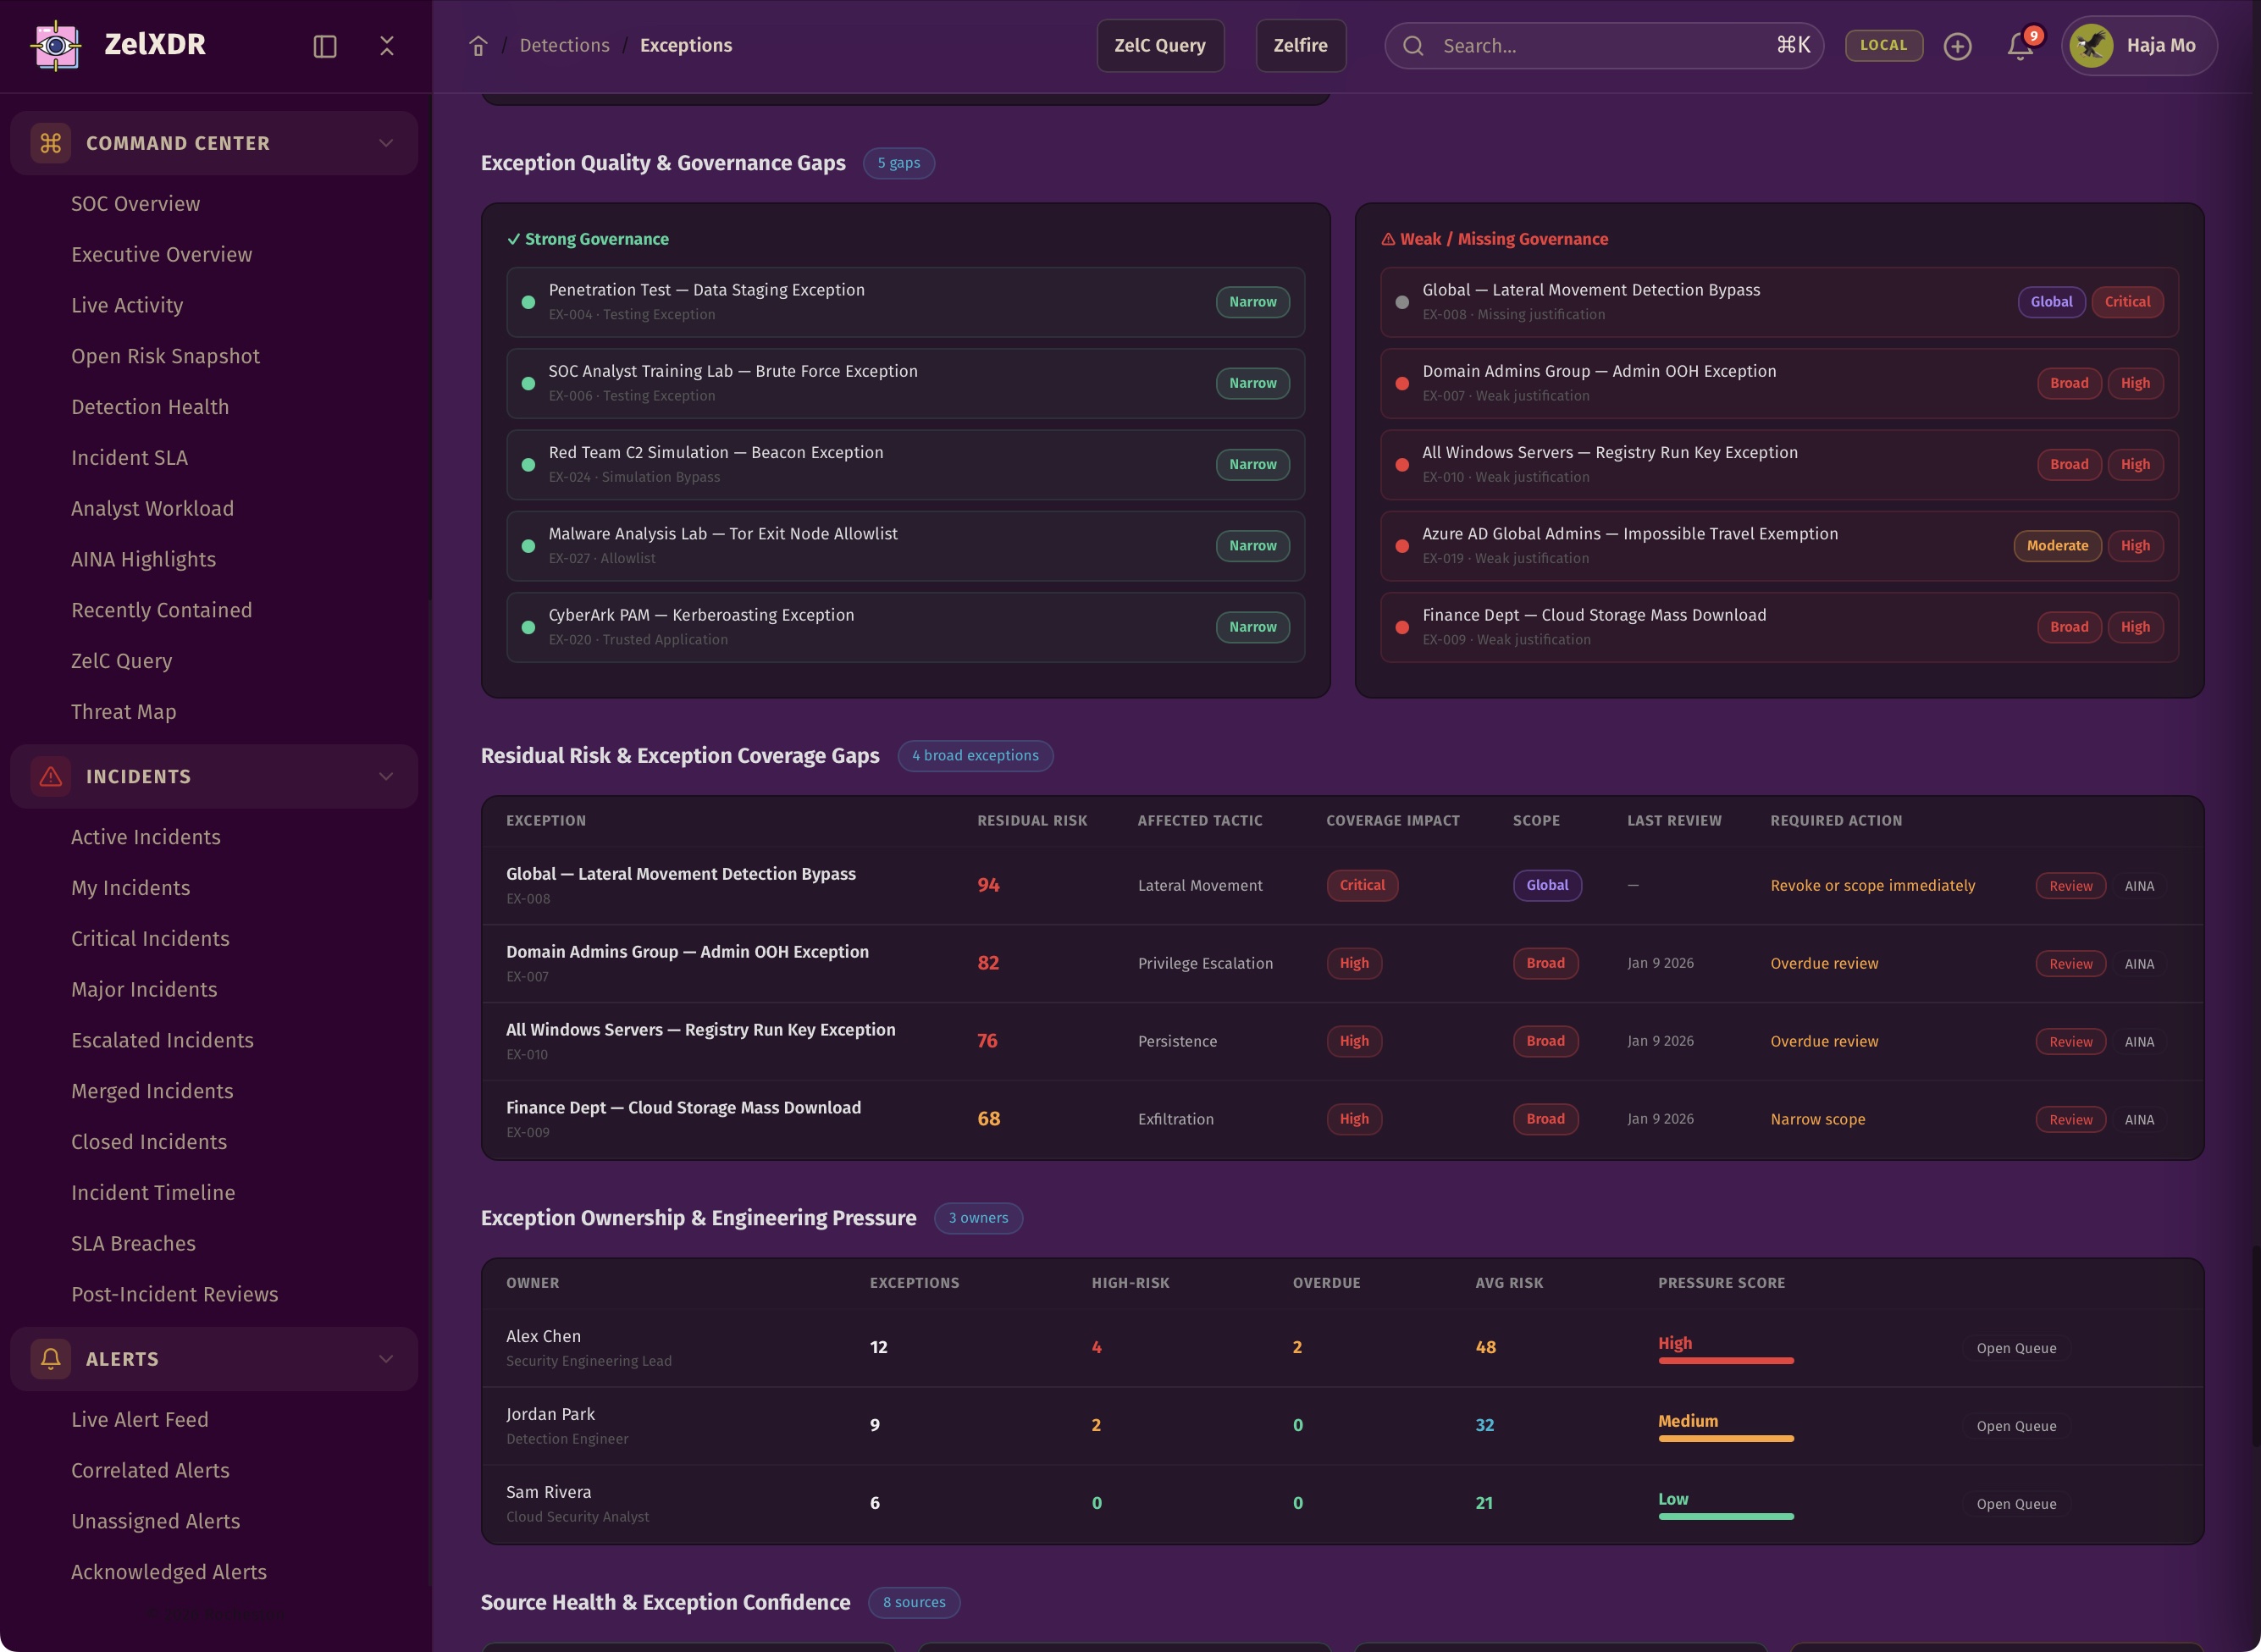
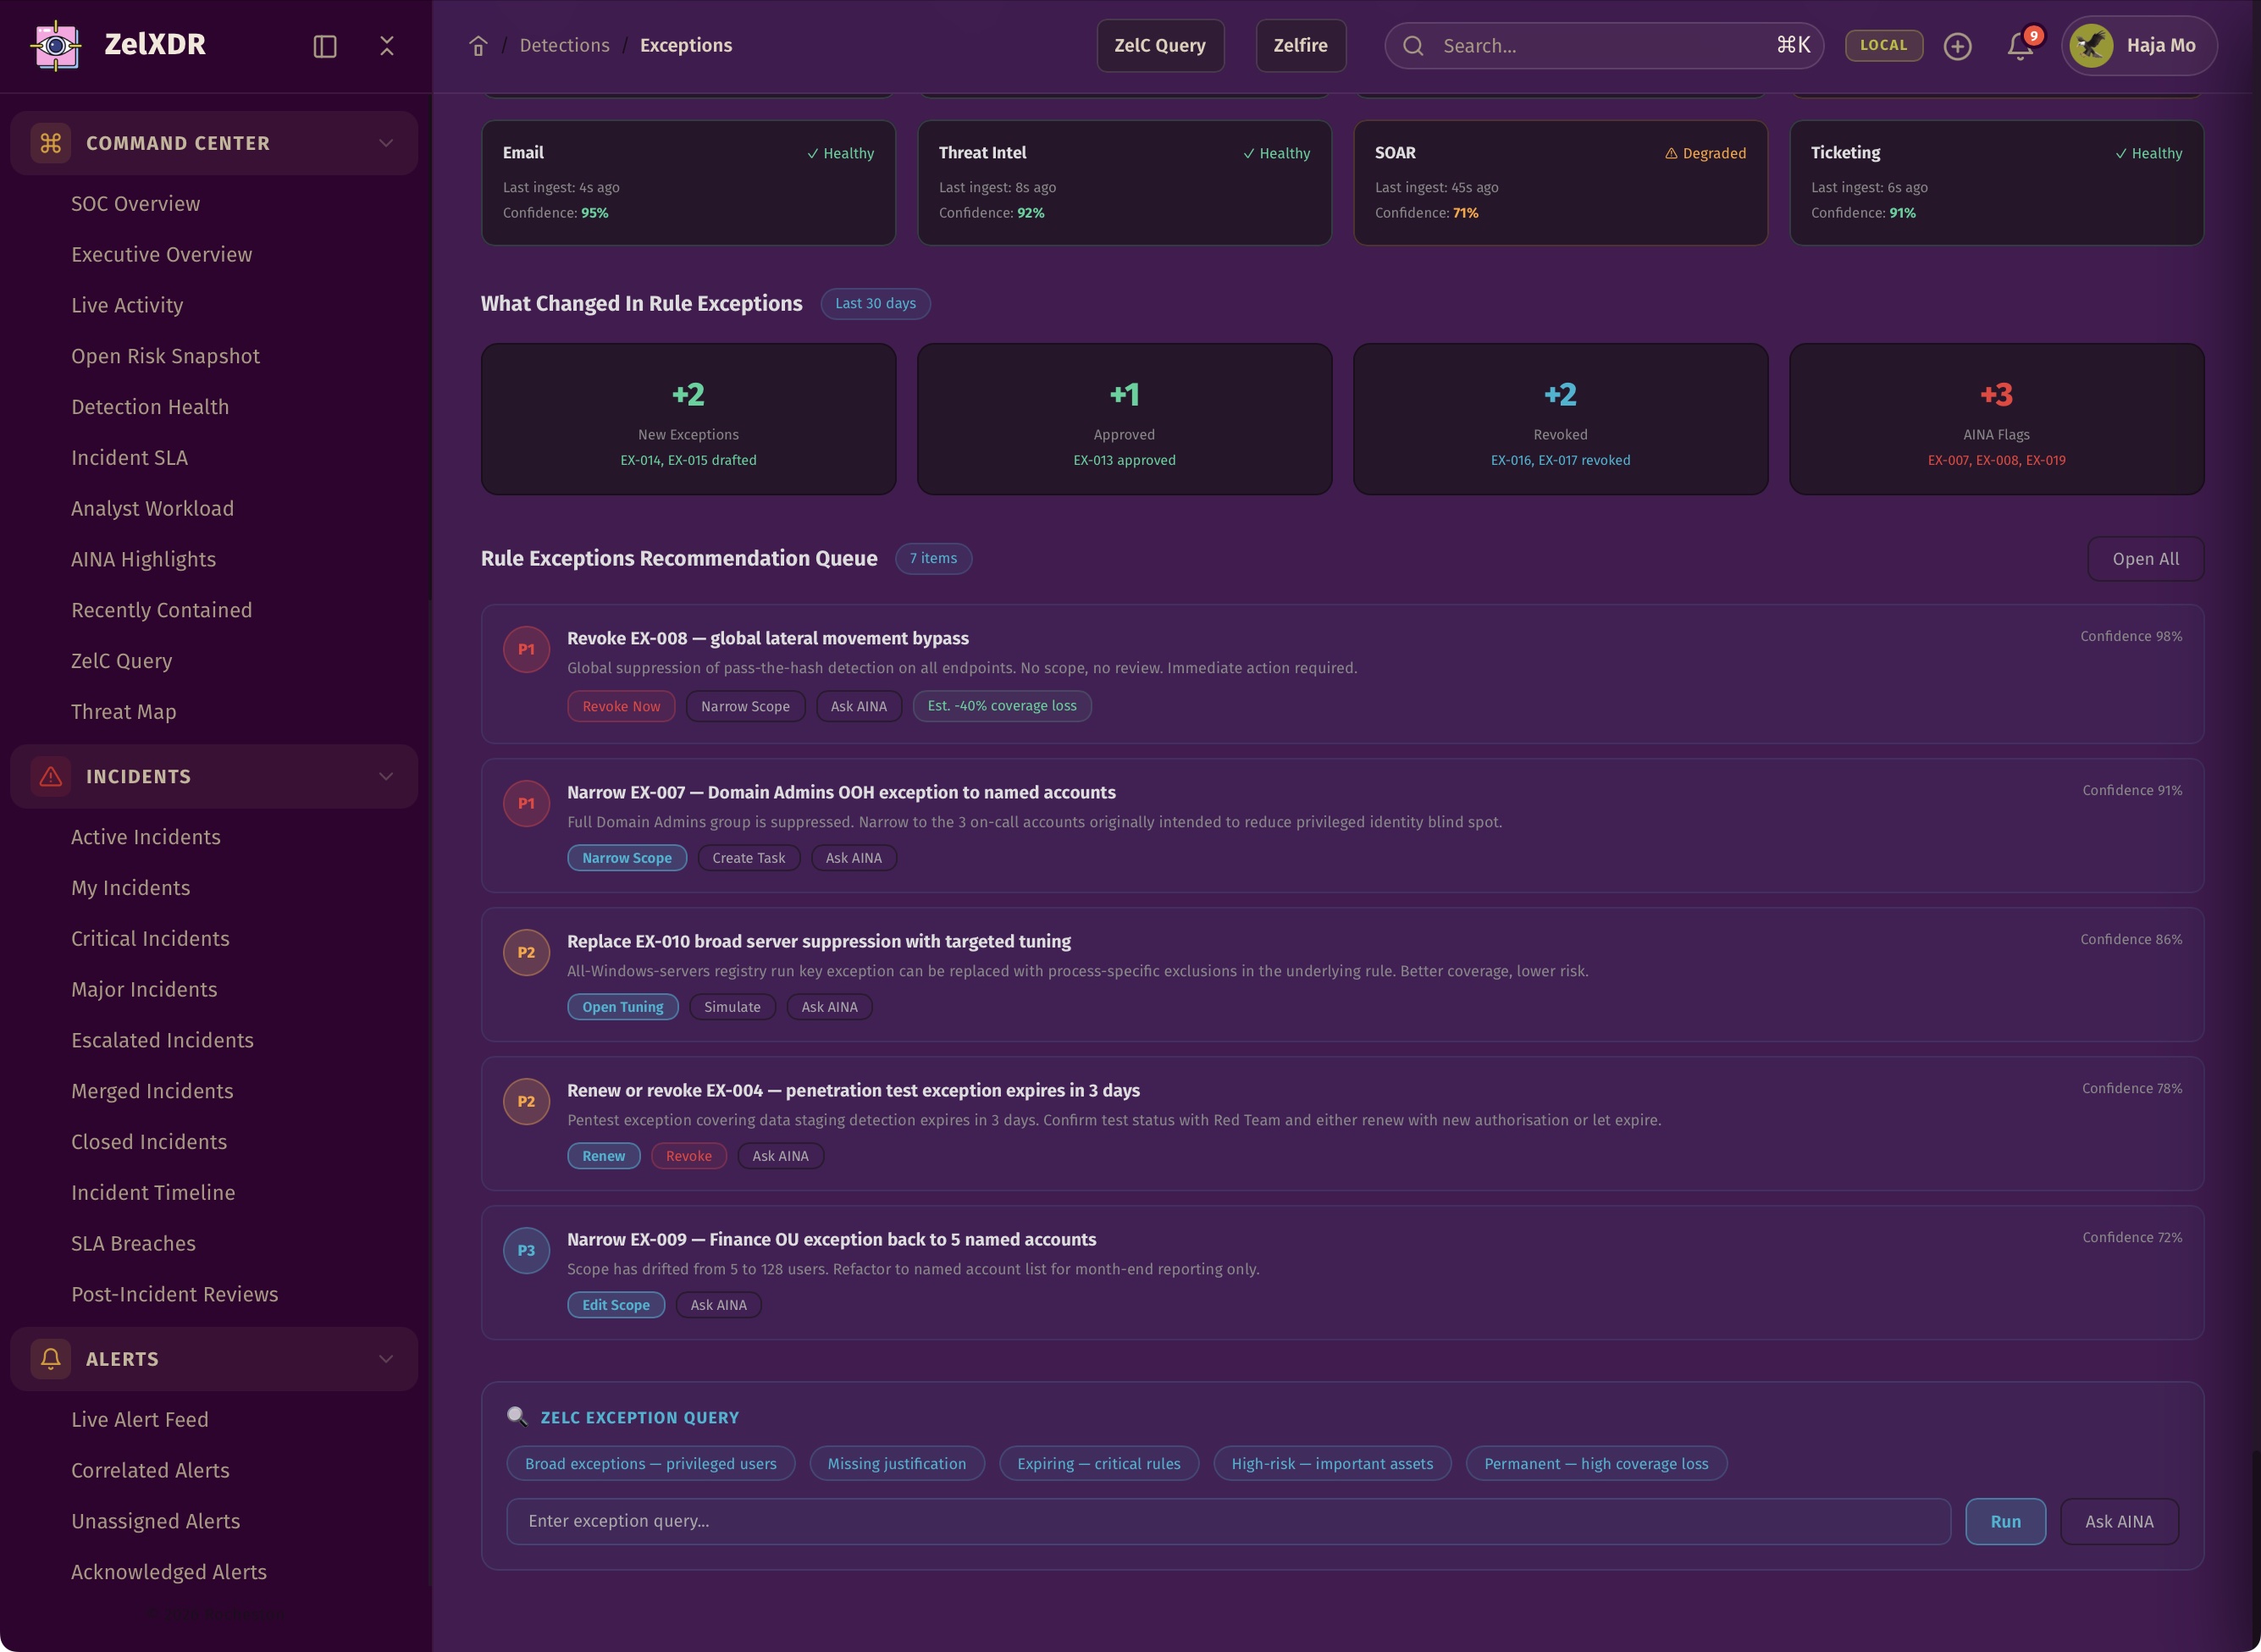
ZelXDR manages exceptions with scope, expiration, review, ownership, and impact visibility so teams can suppress legitimate noise without quietly creating dangerous blind spots.
Every exception should be deliberate, visible, and reversible.
Every rule, mapping, severity update, logic change, exception change, and deployment event can be tracked inside ZelXDR, creating an audit-ready history of platform change.
Change is safer when every decision leaves a trace.
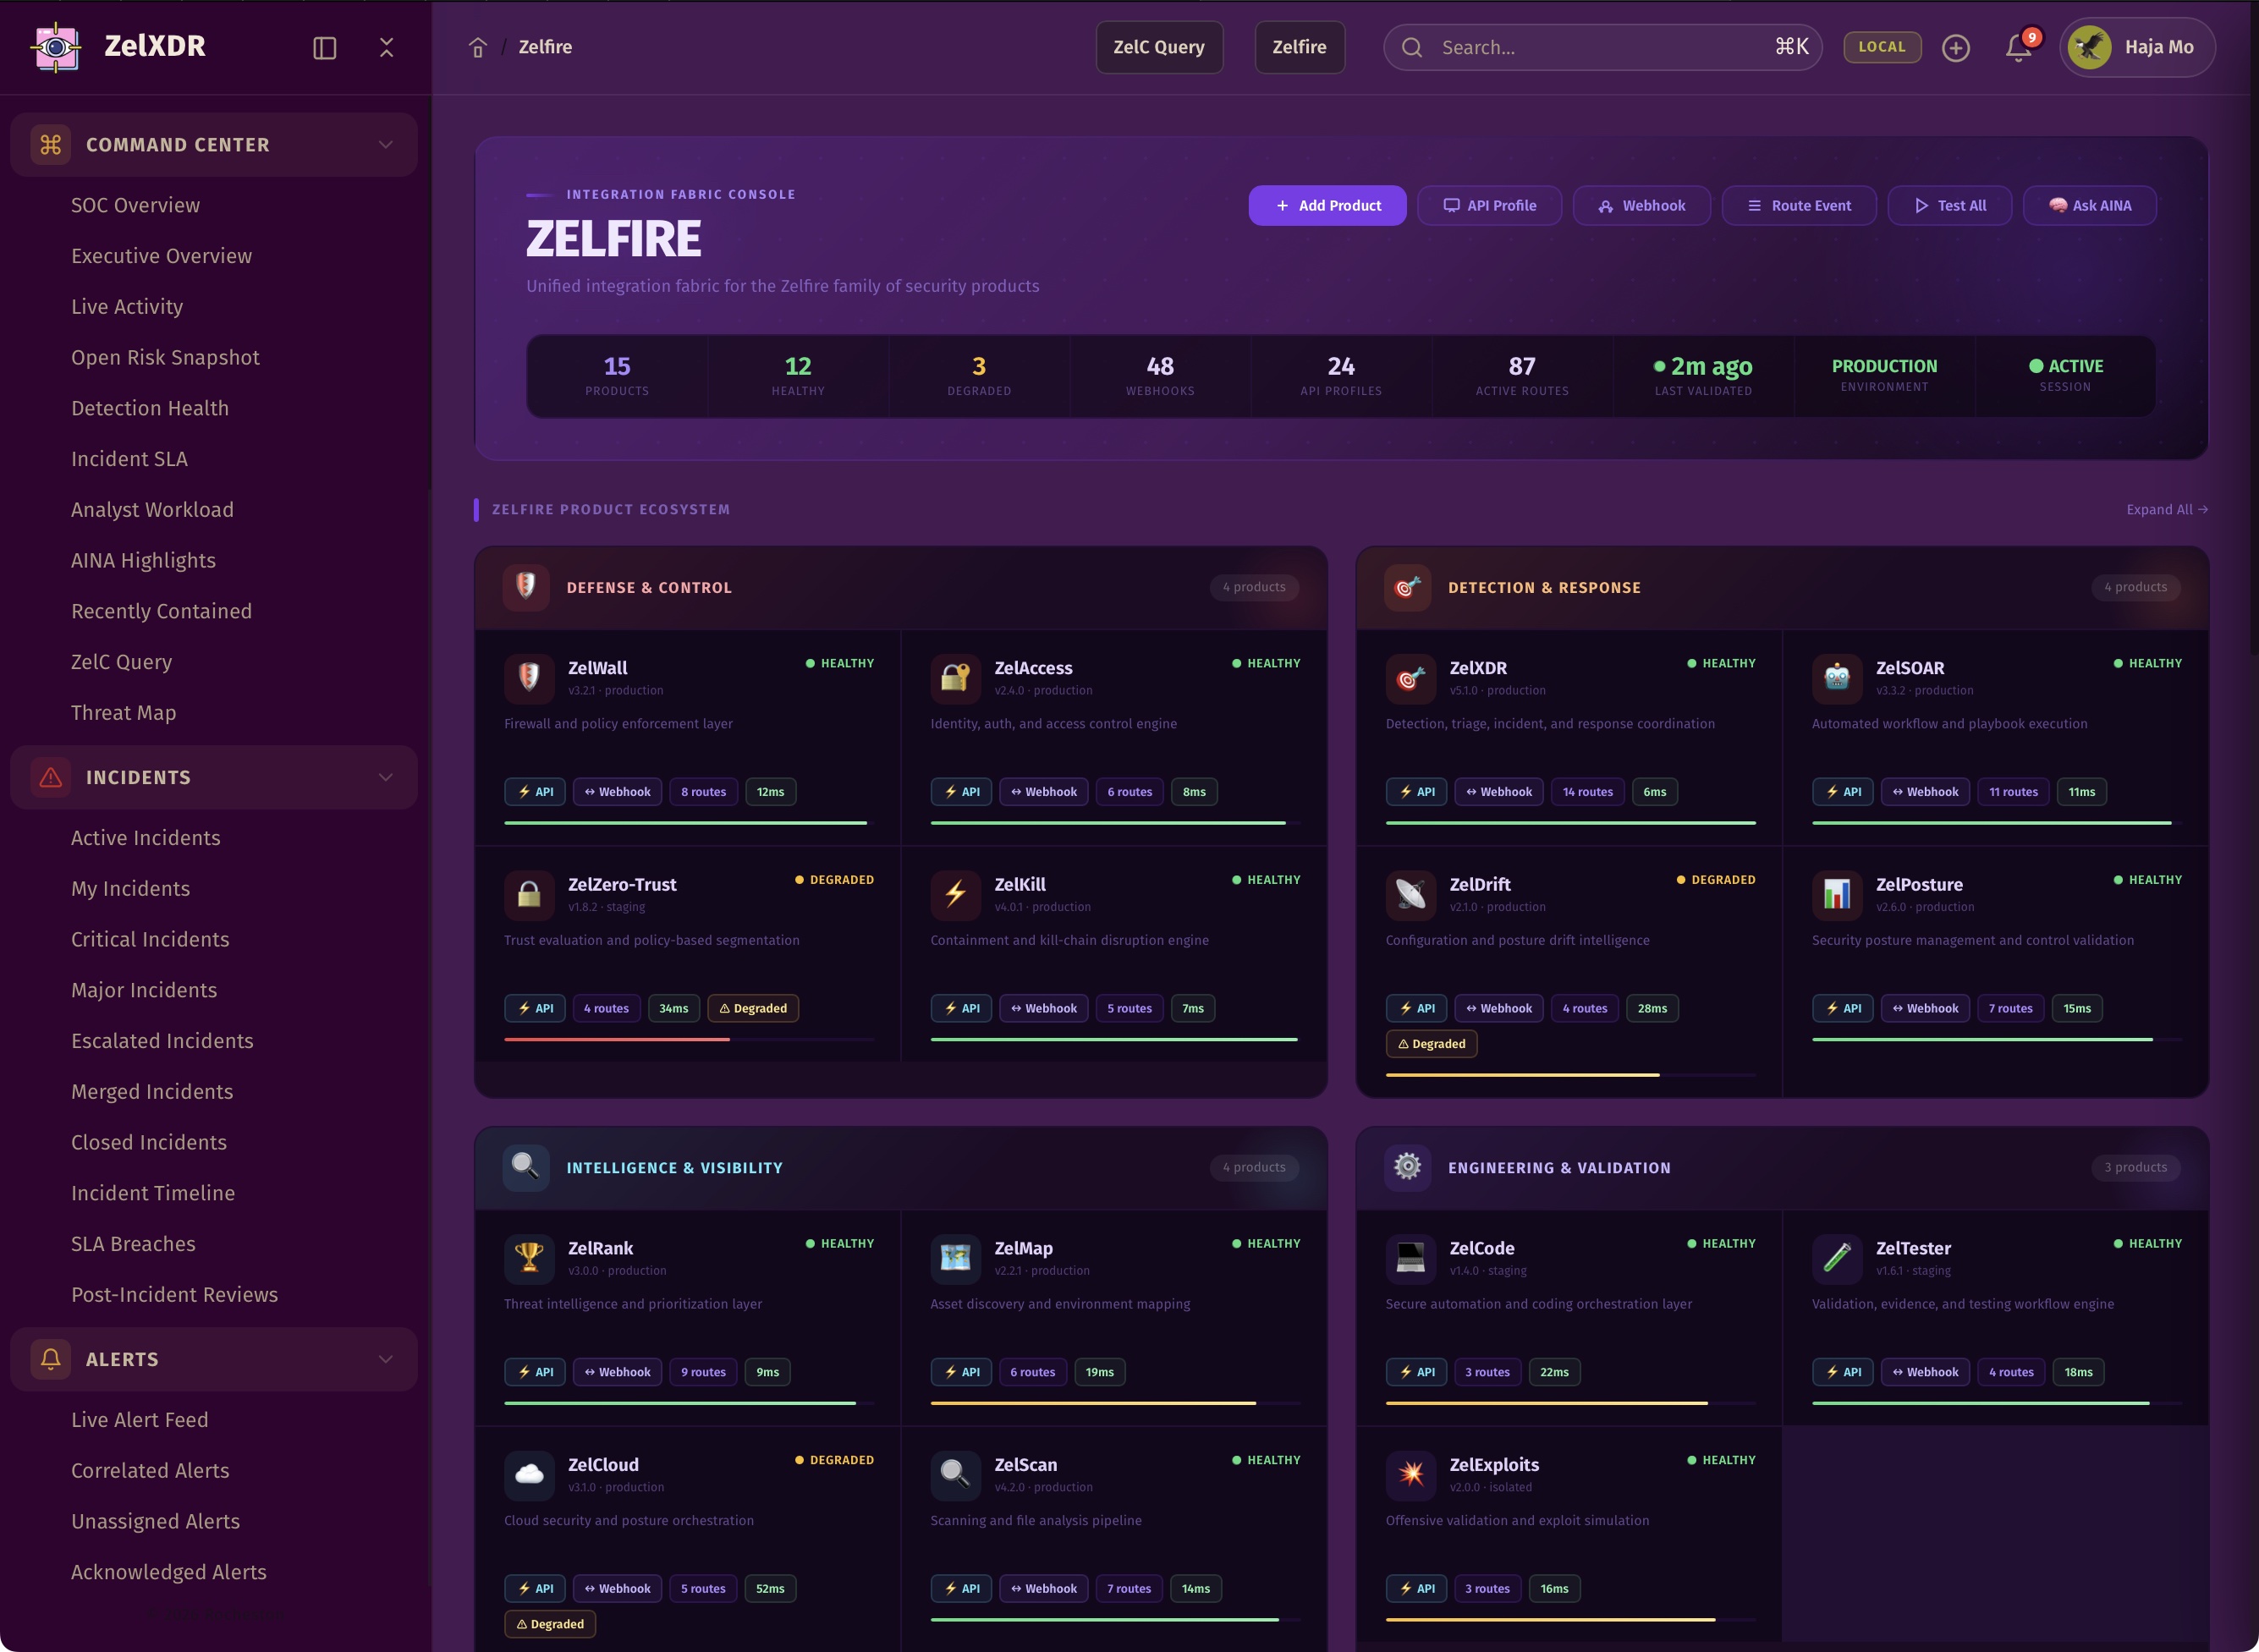
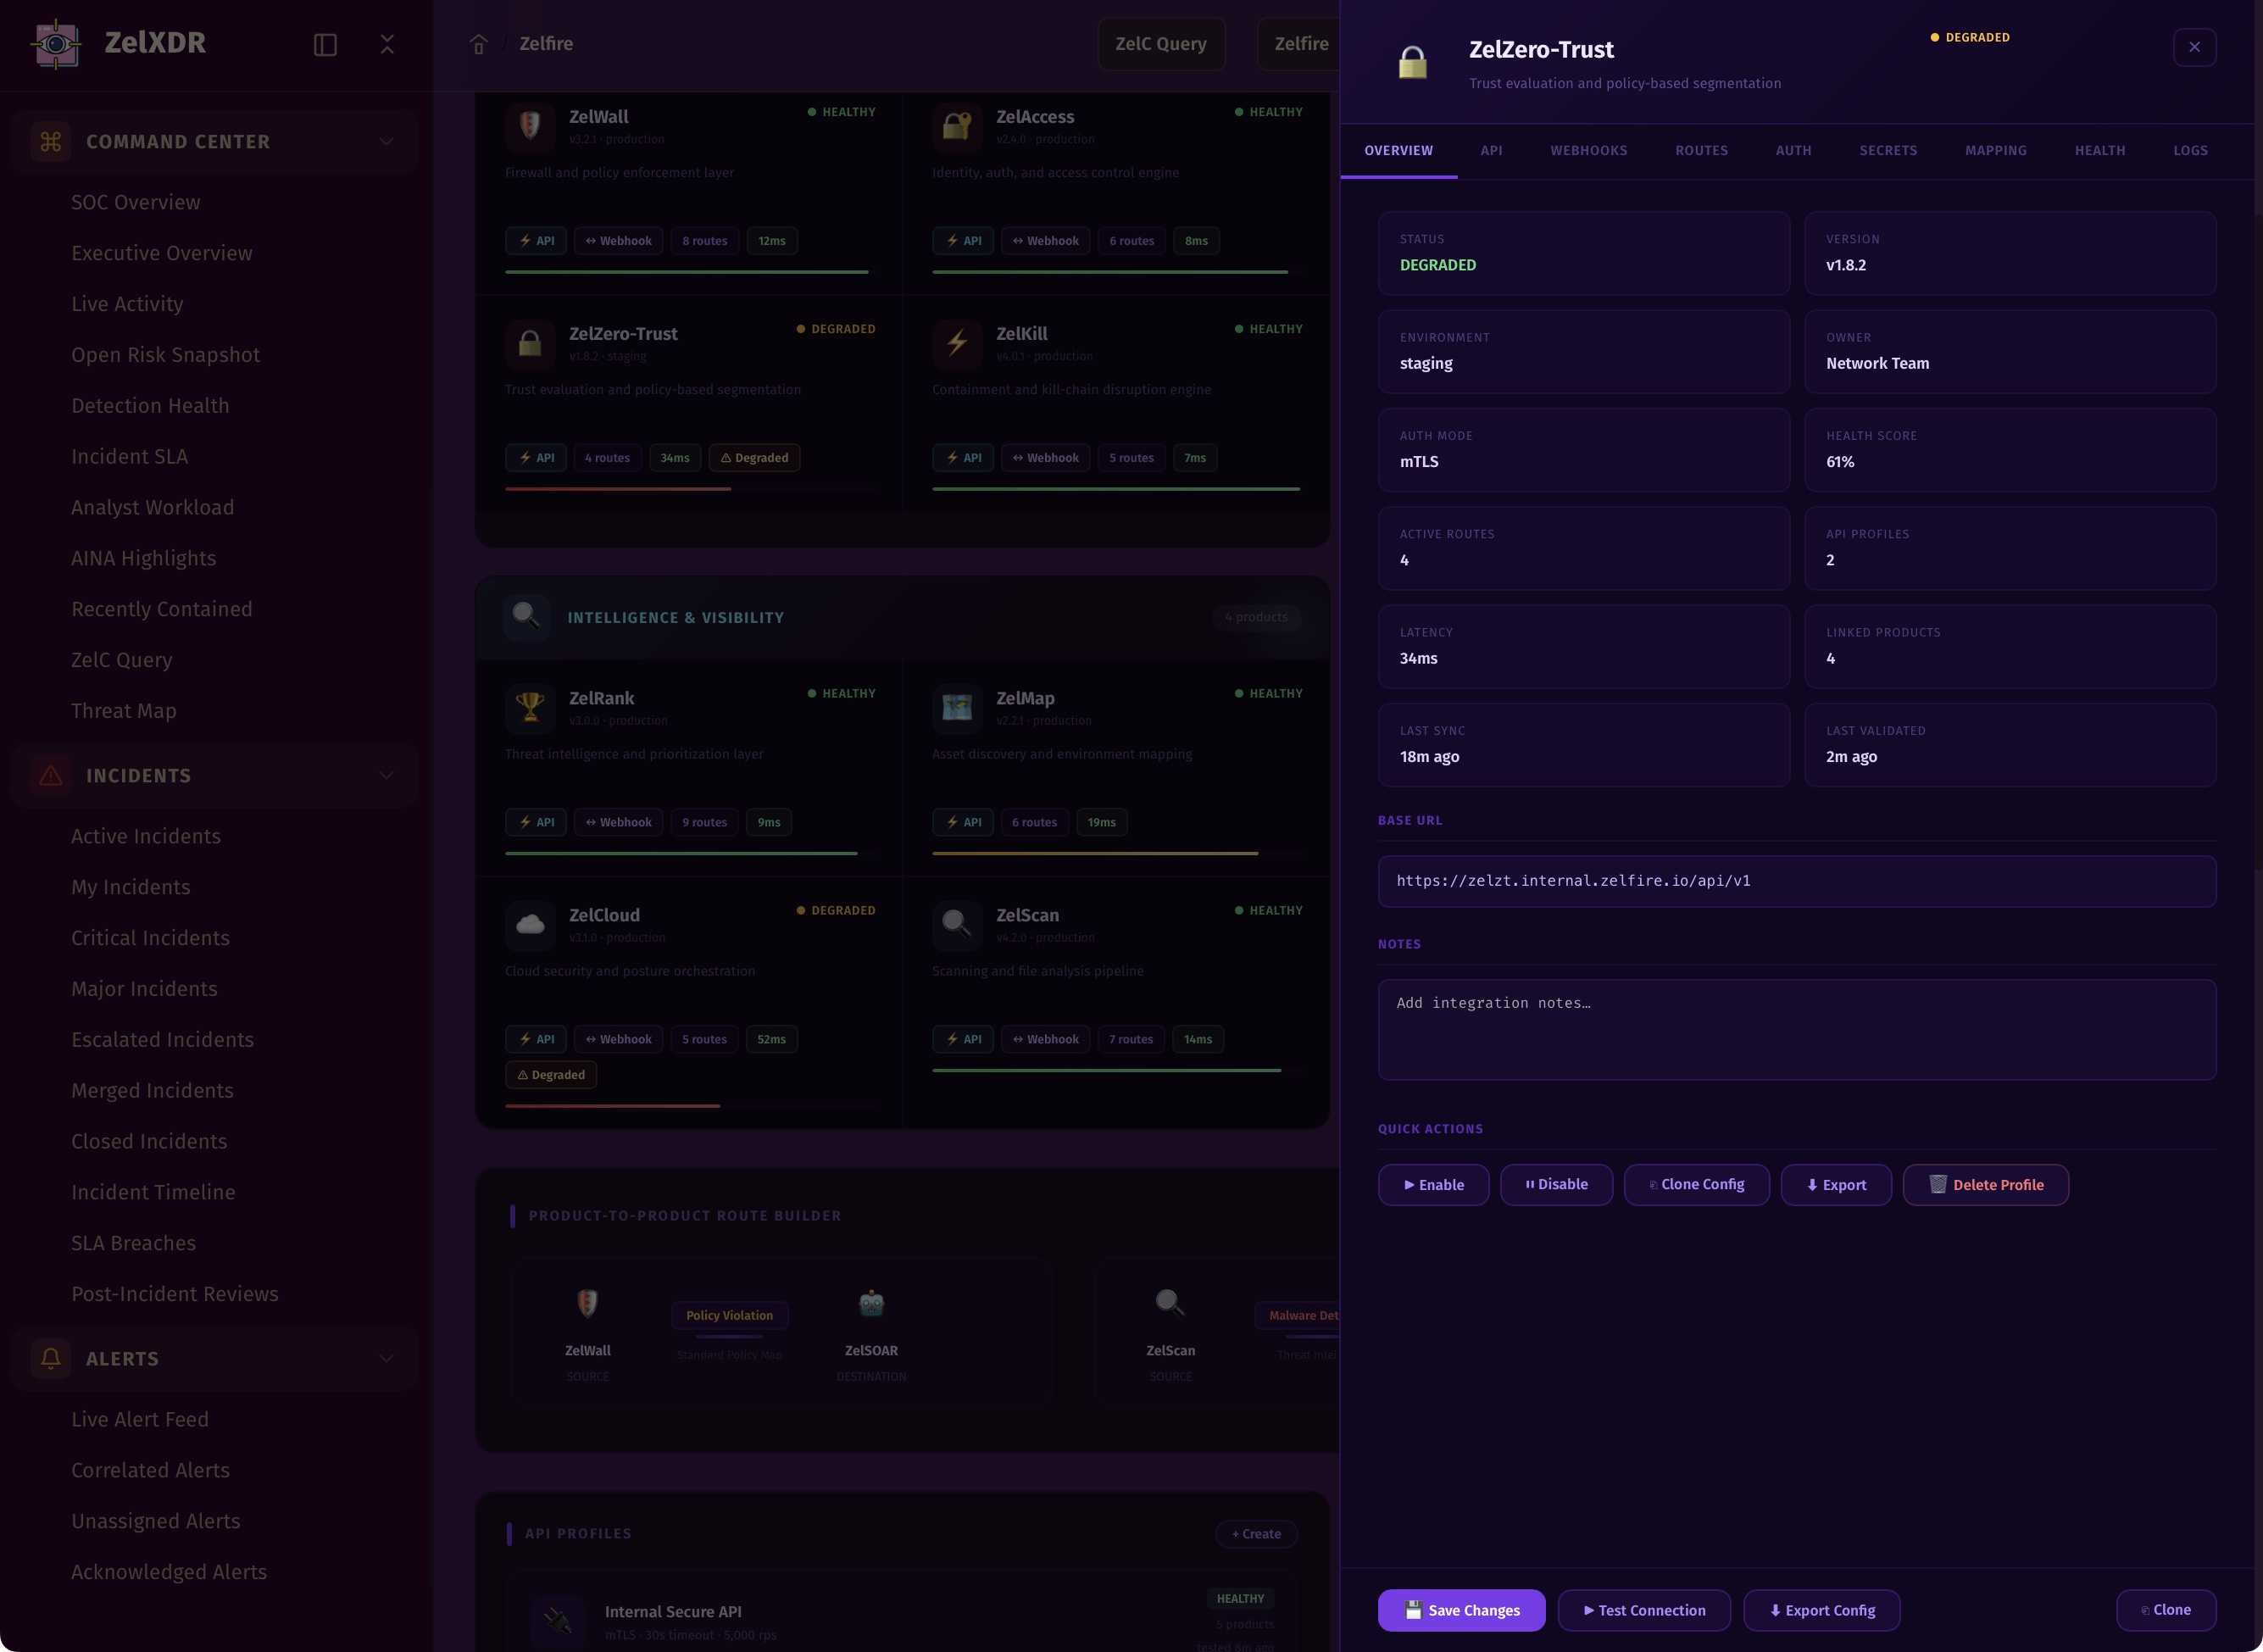
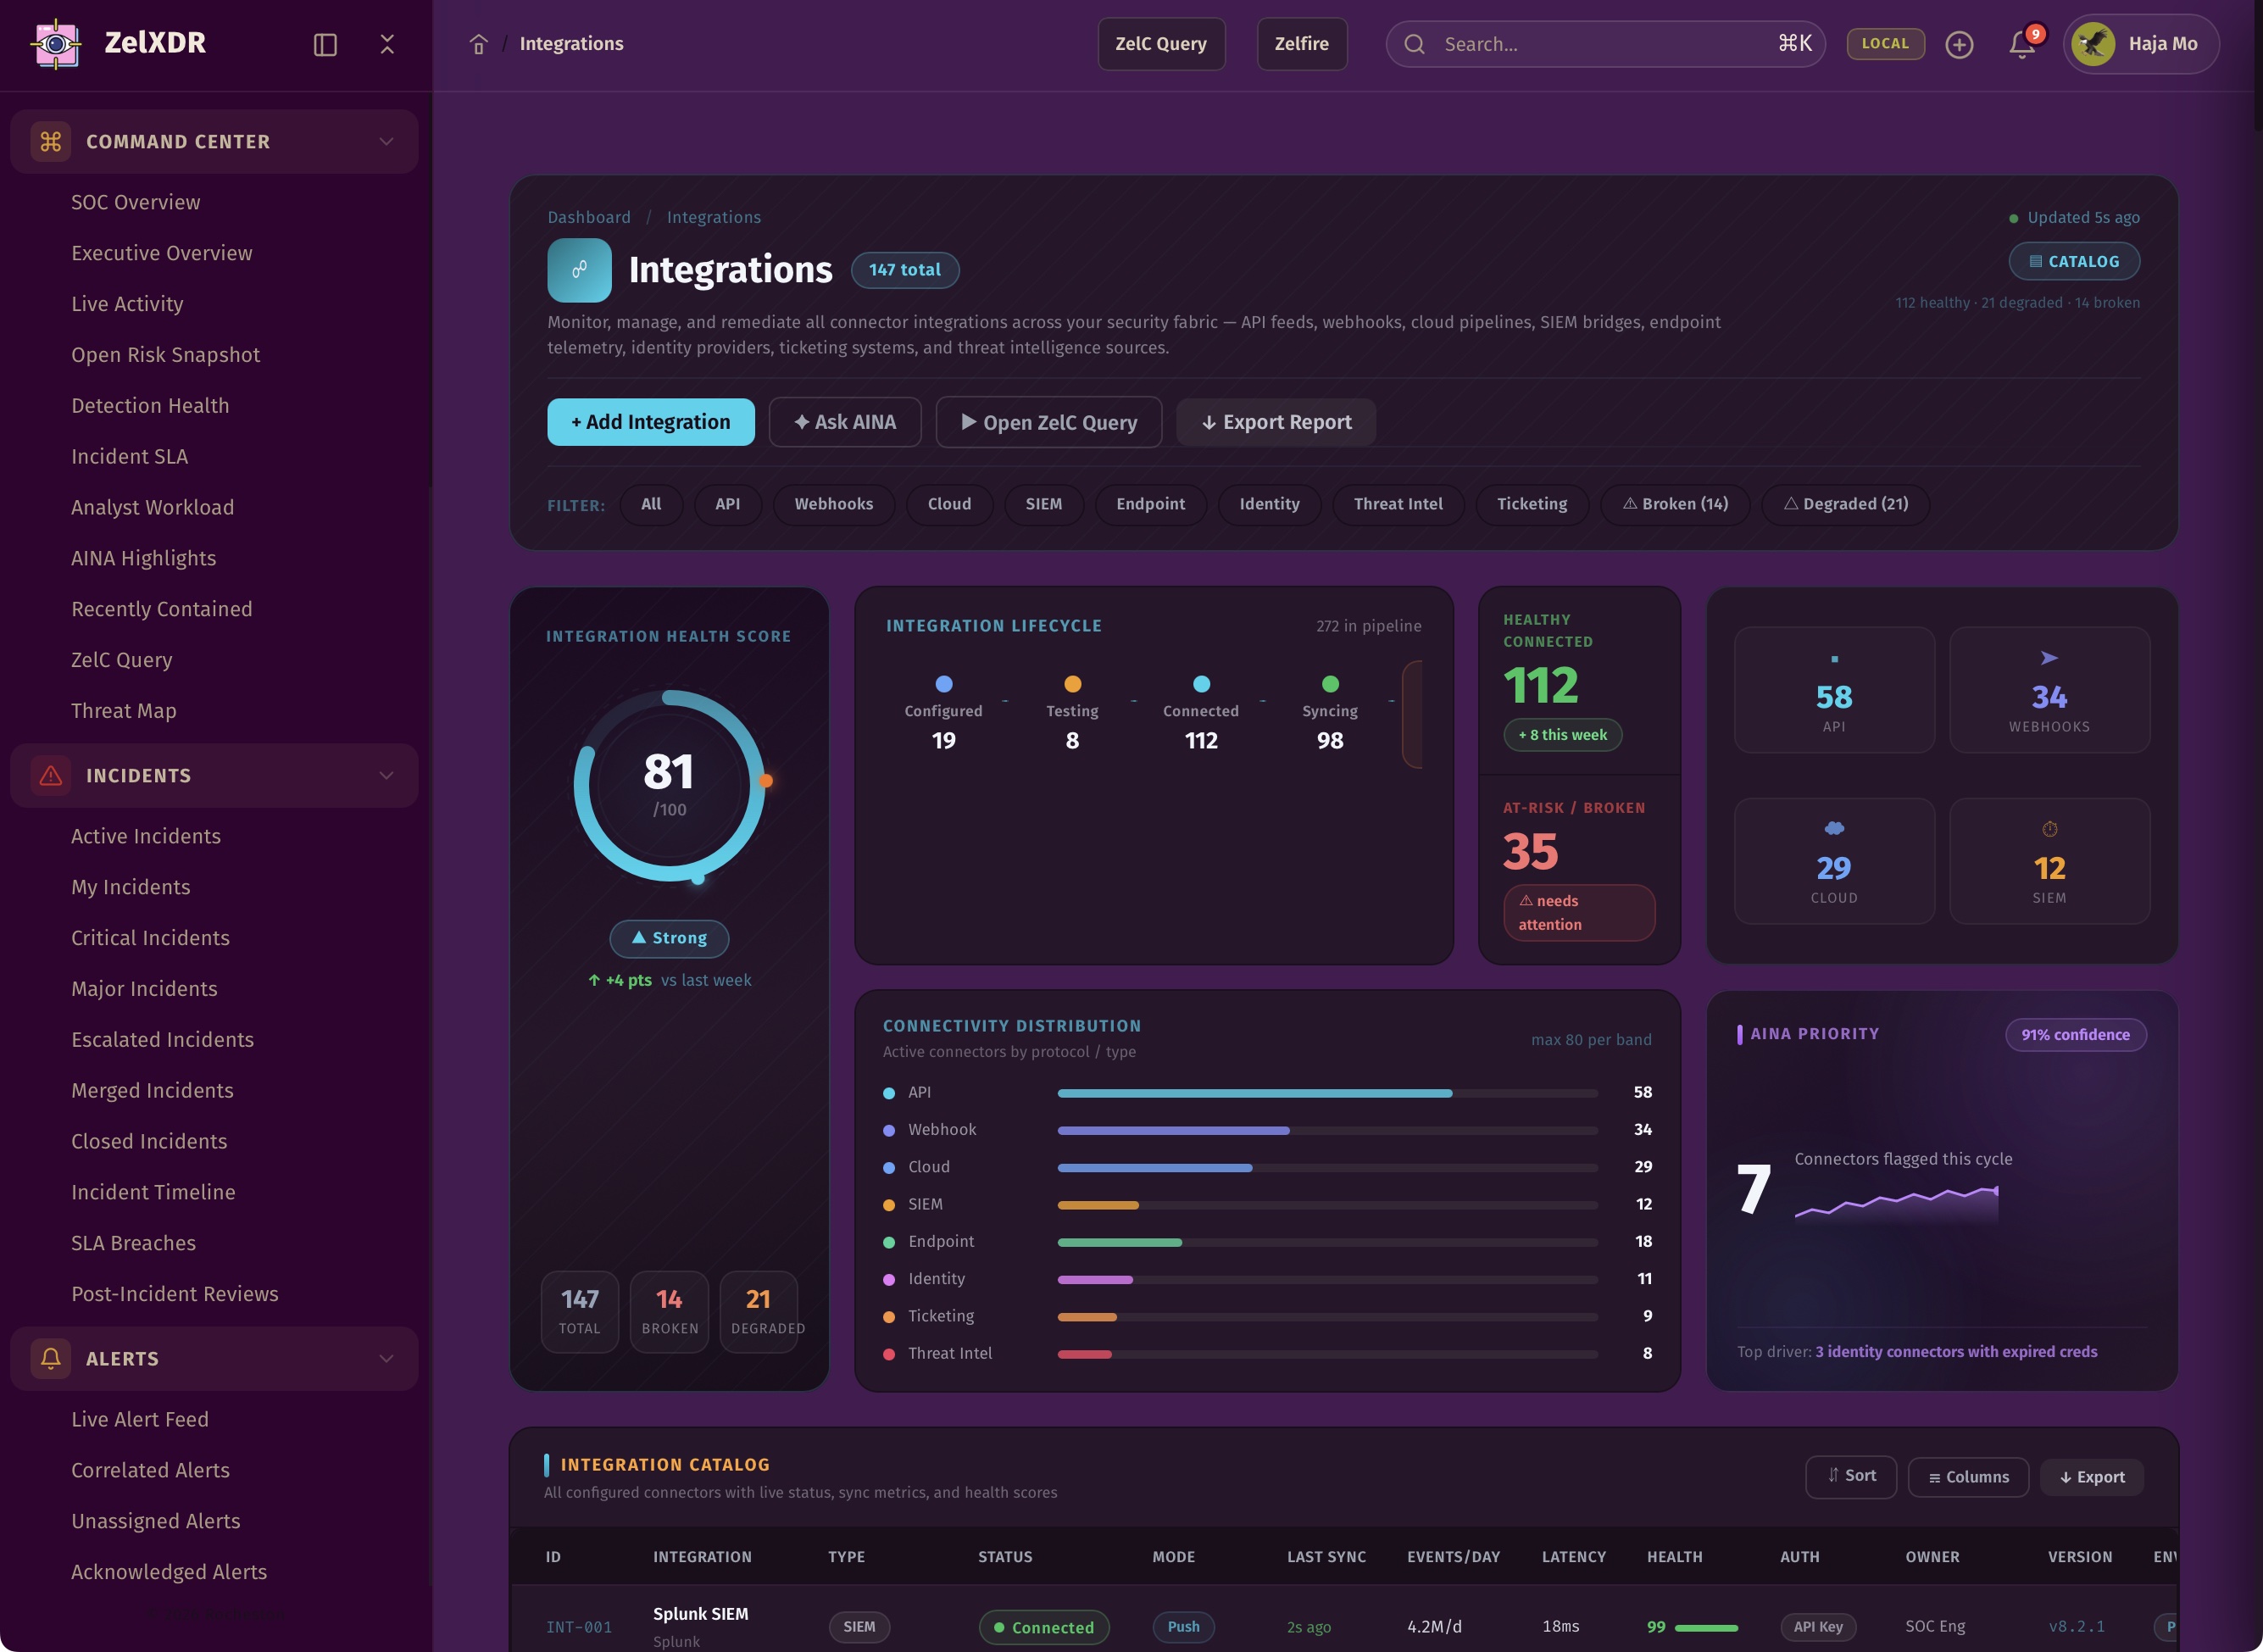
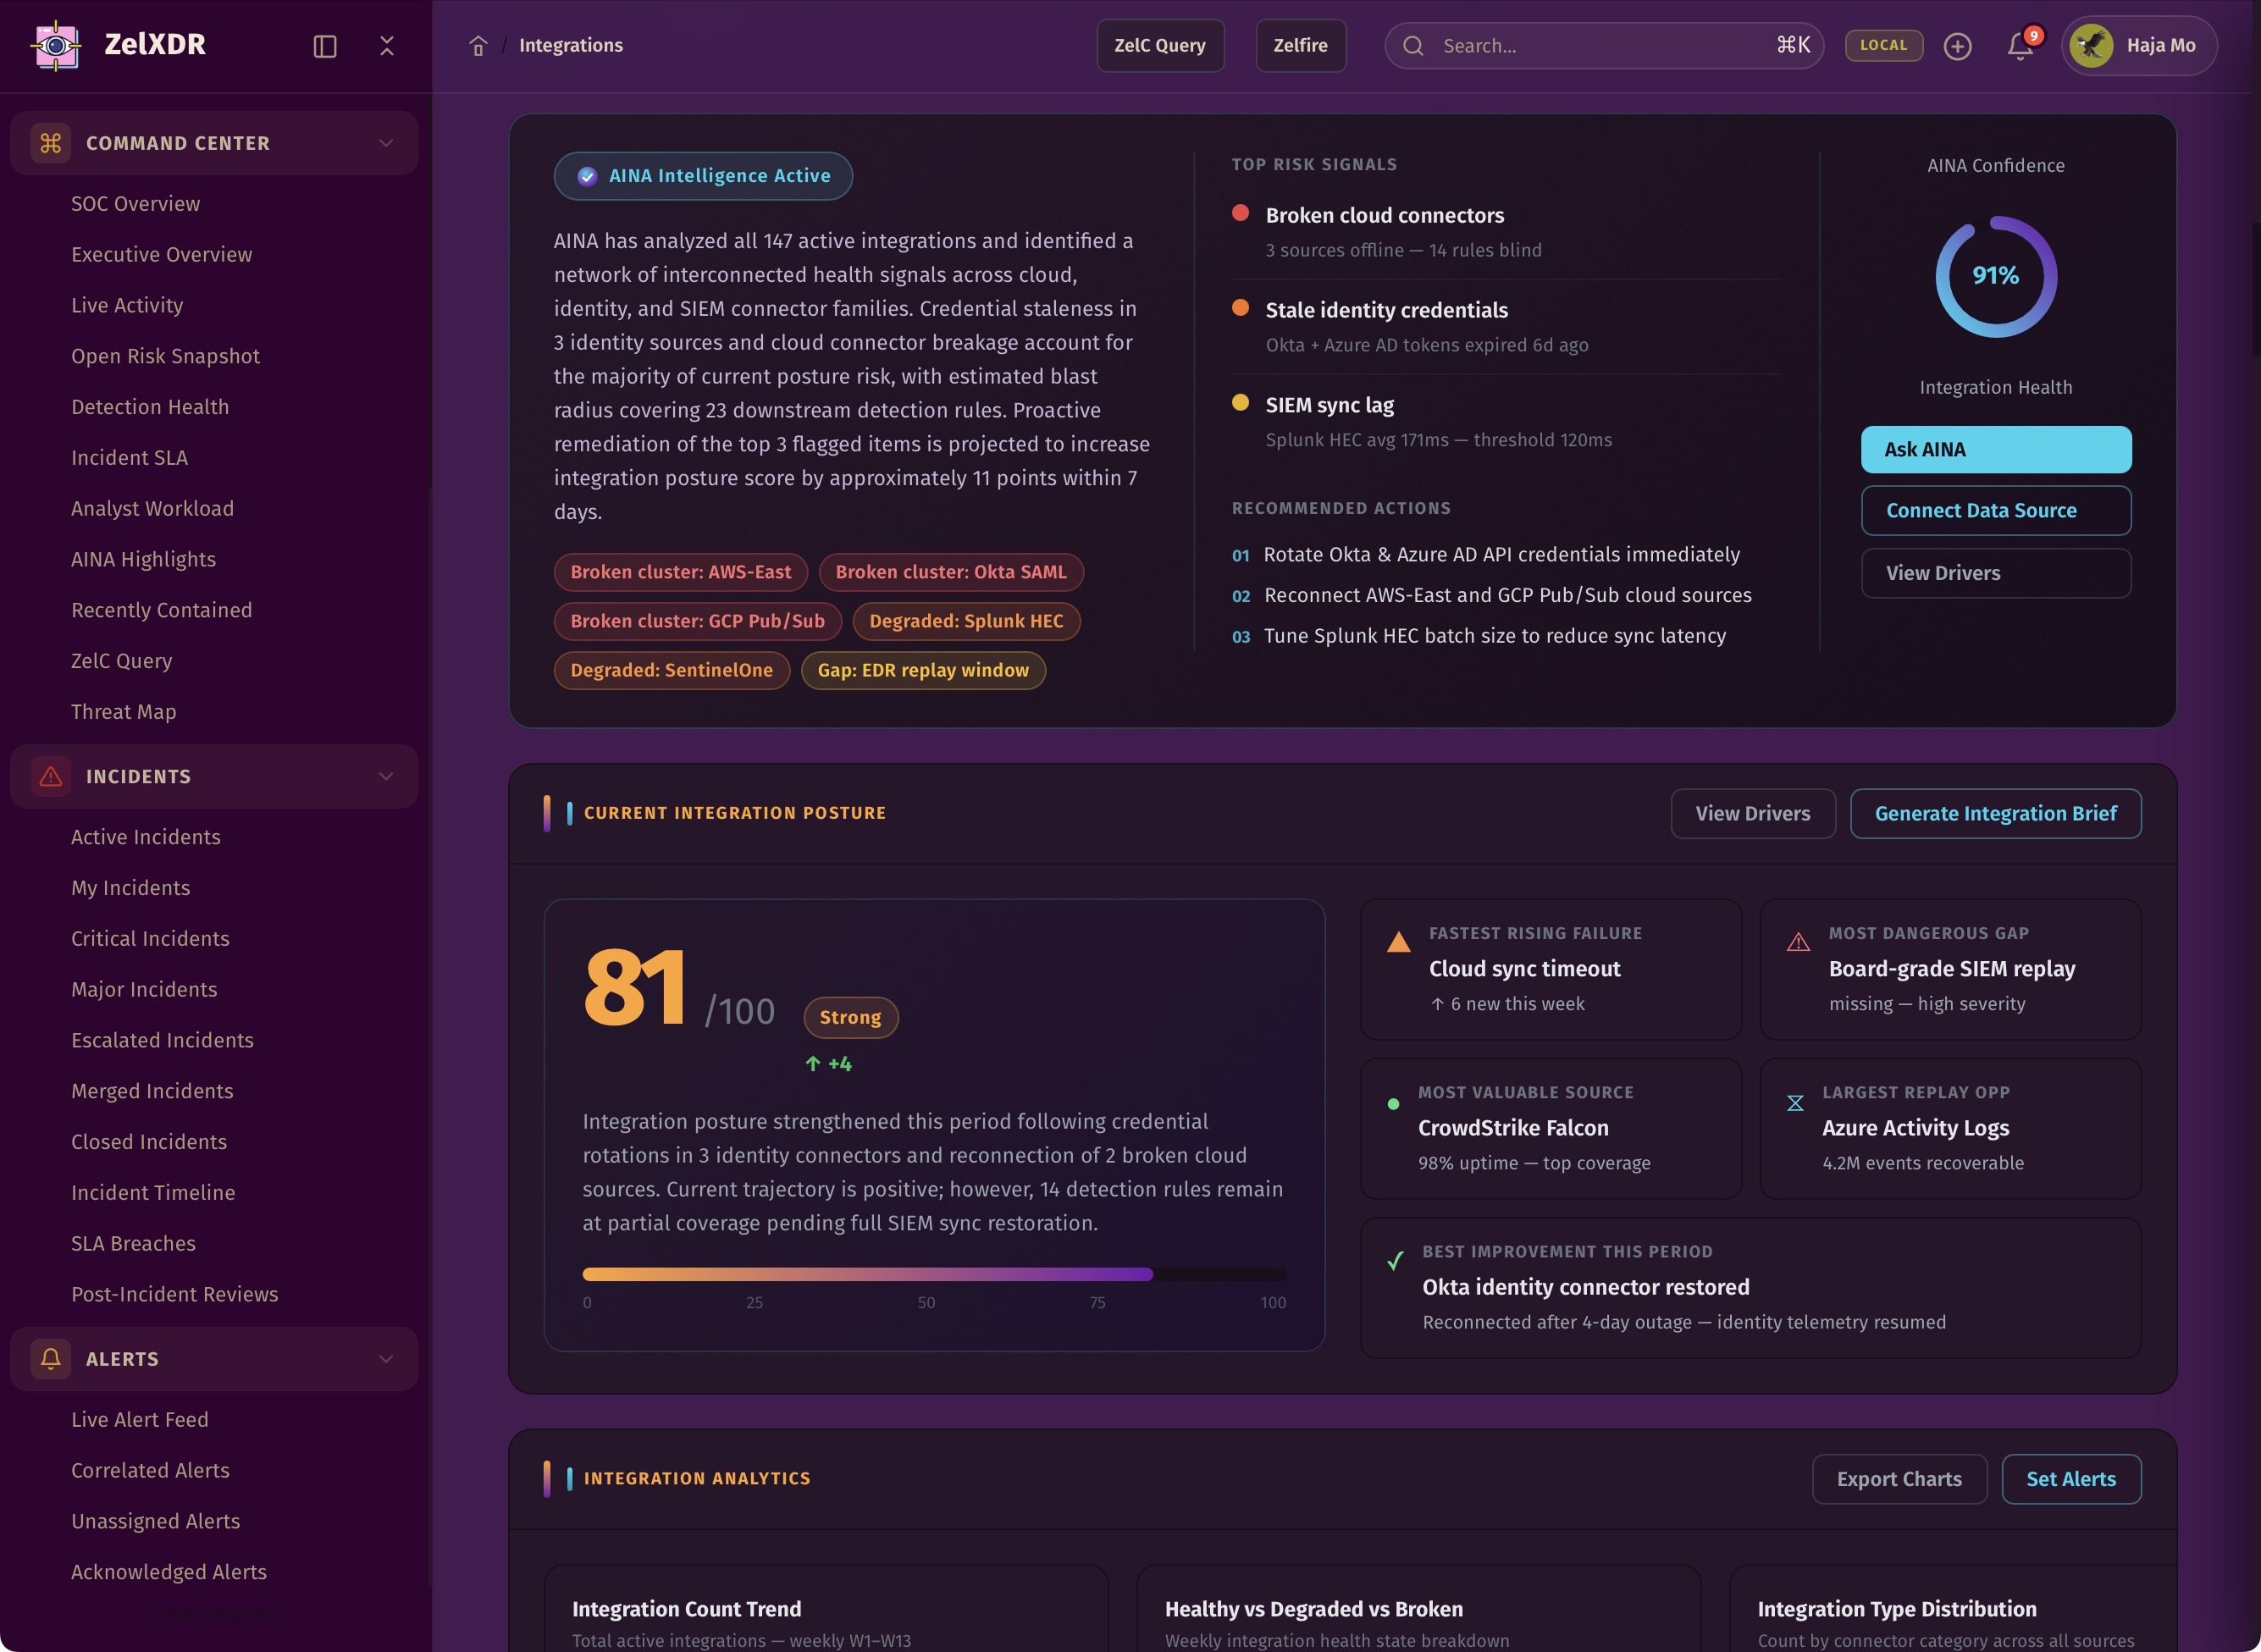
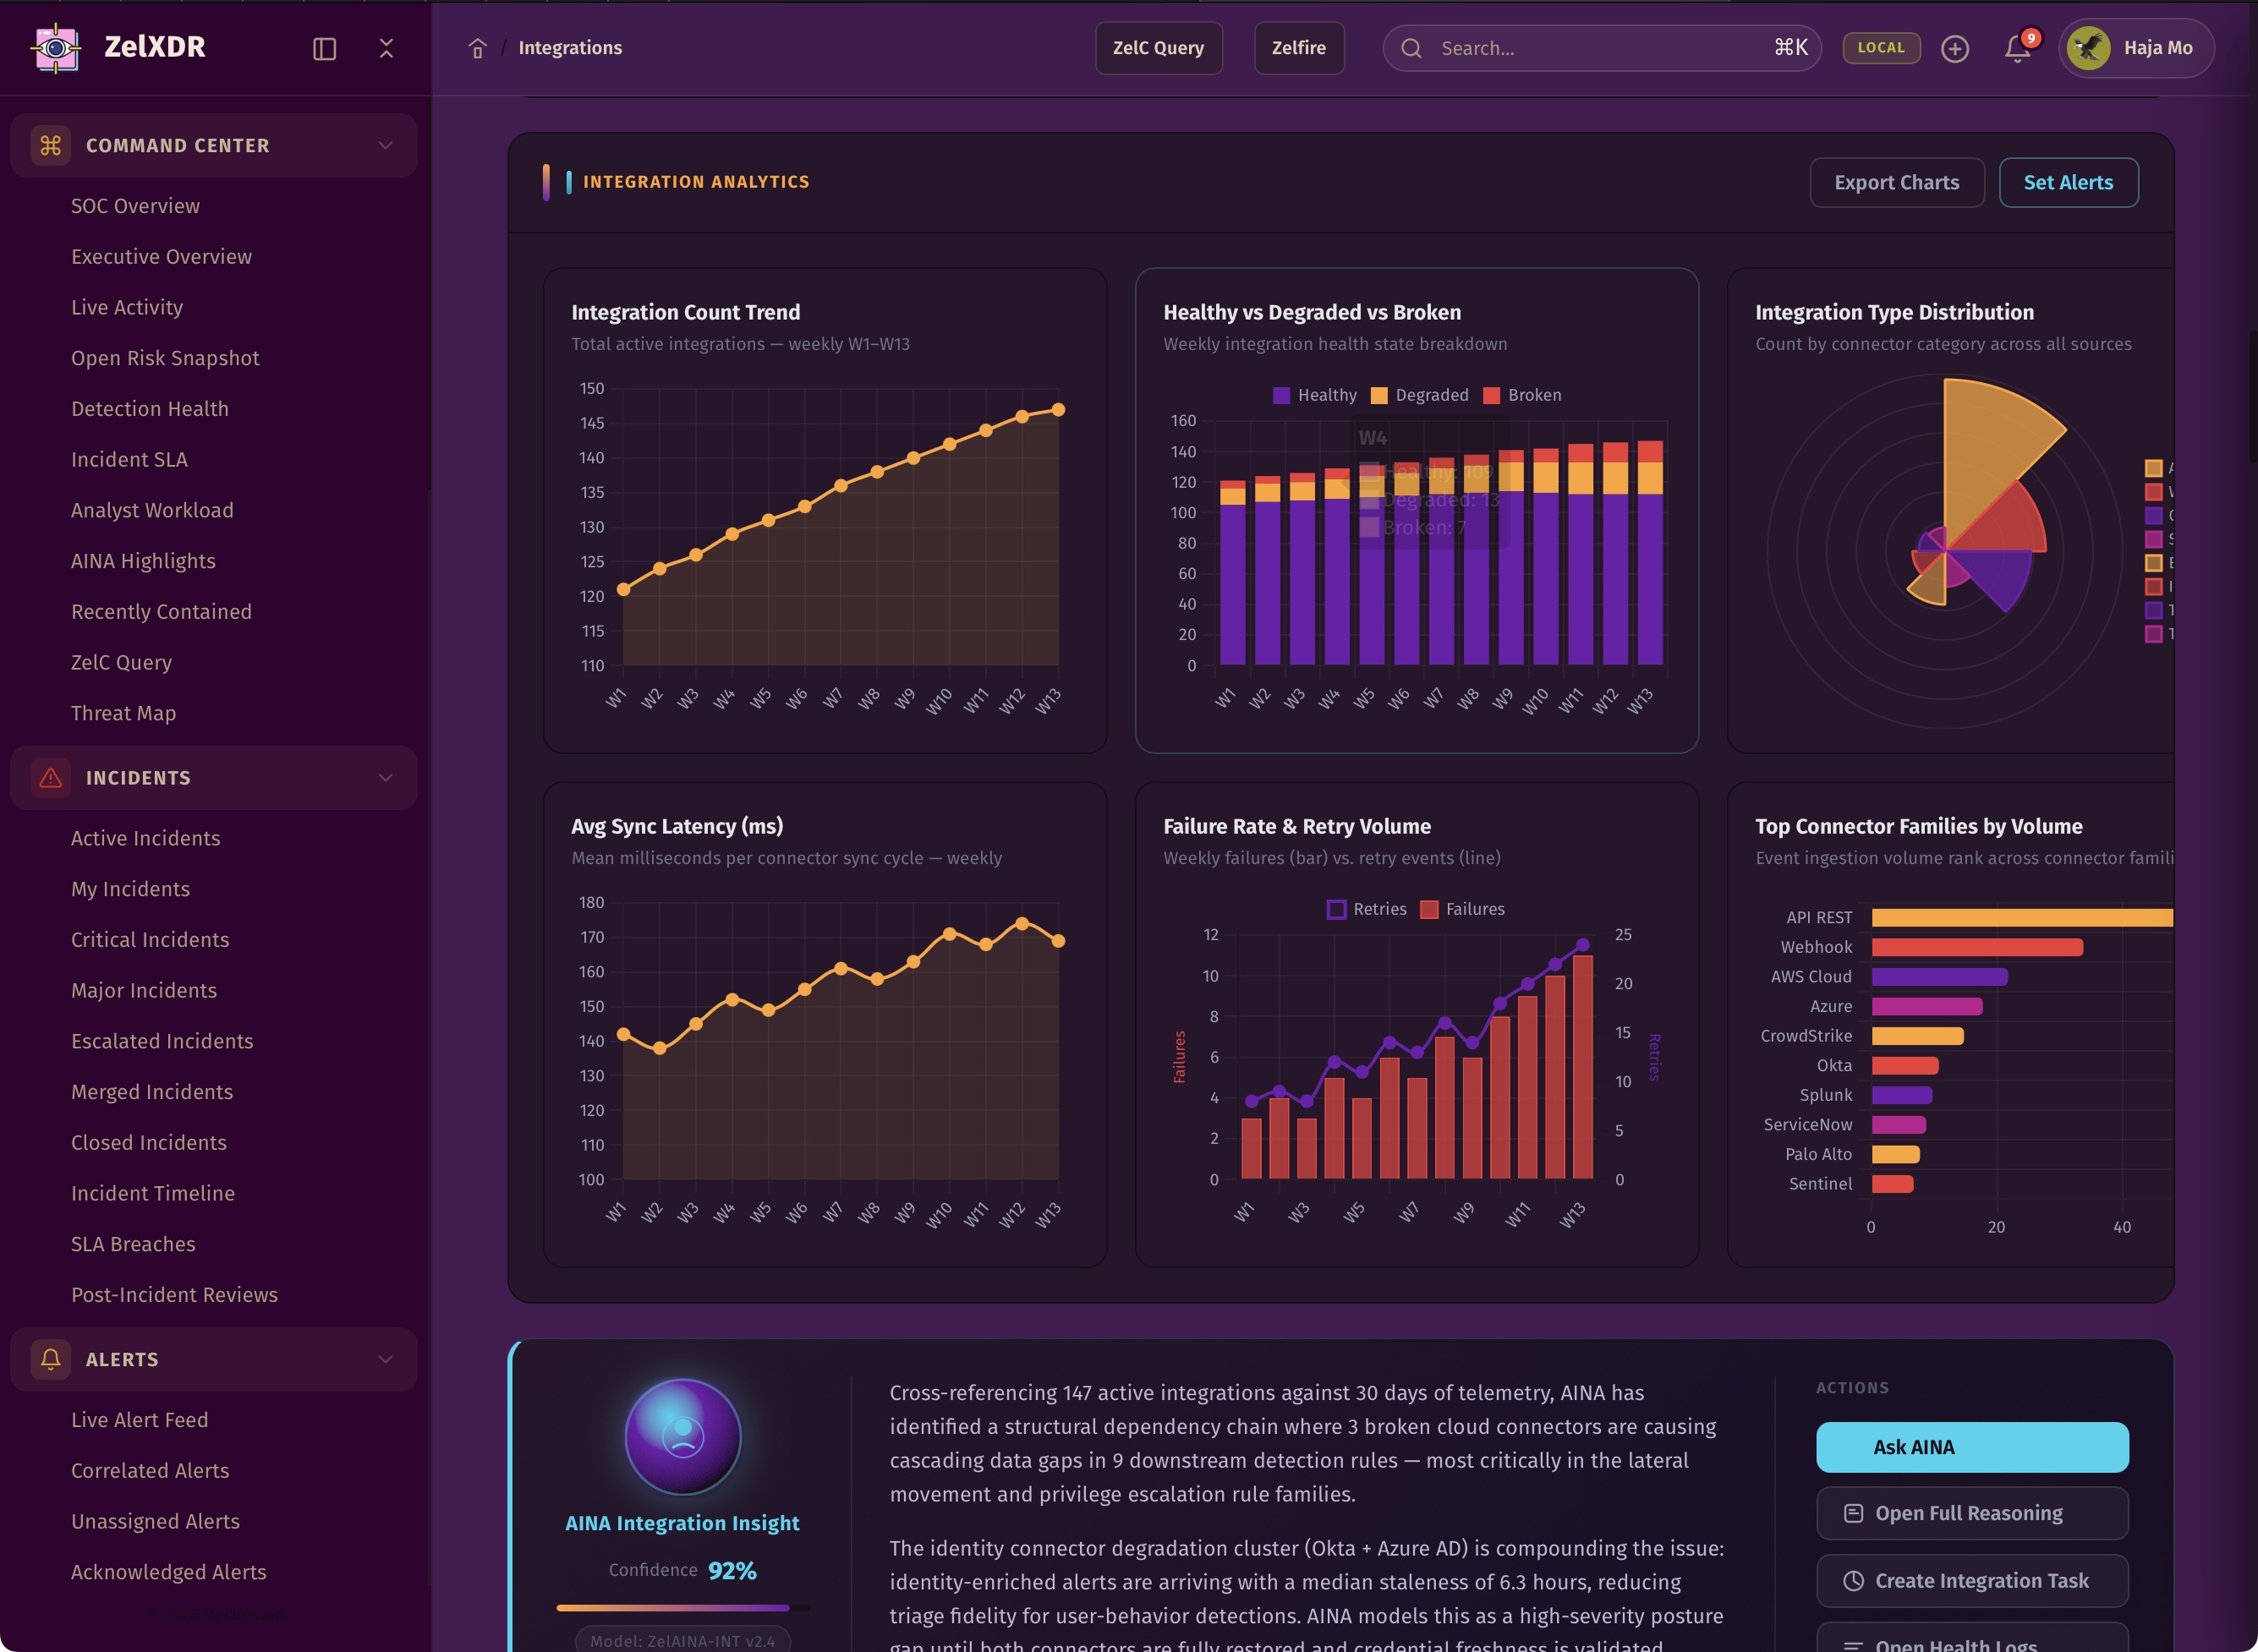
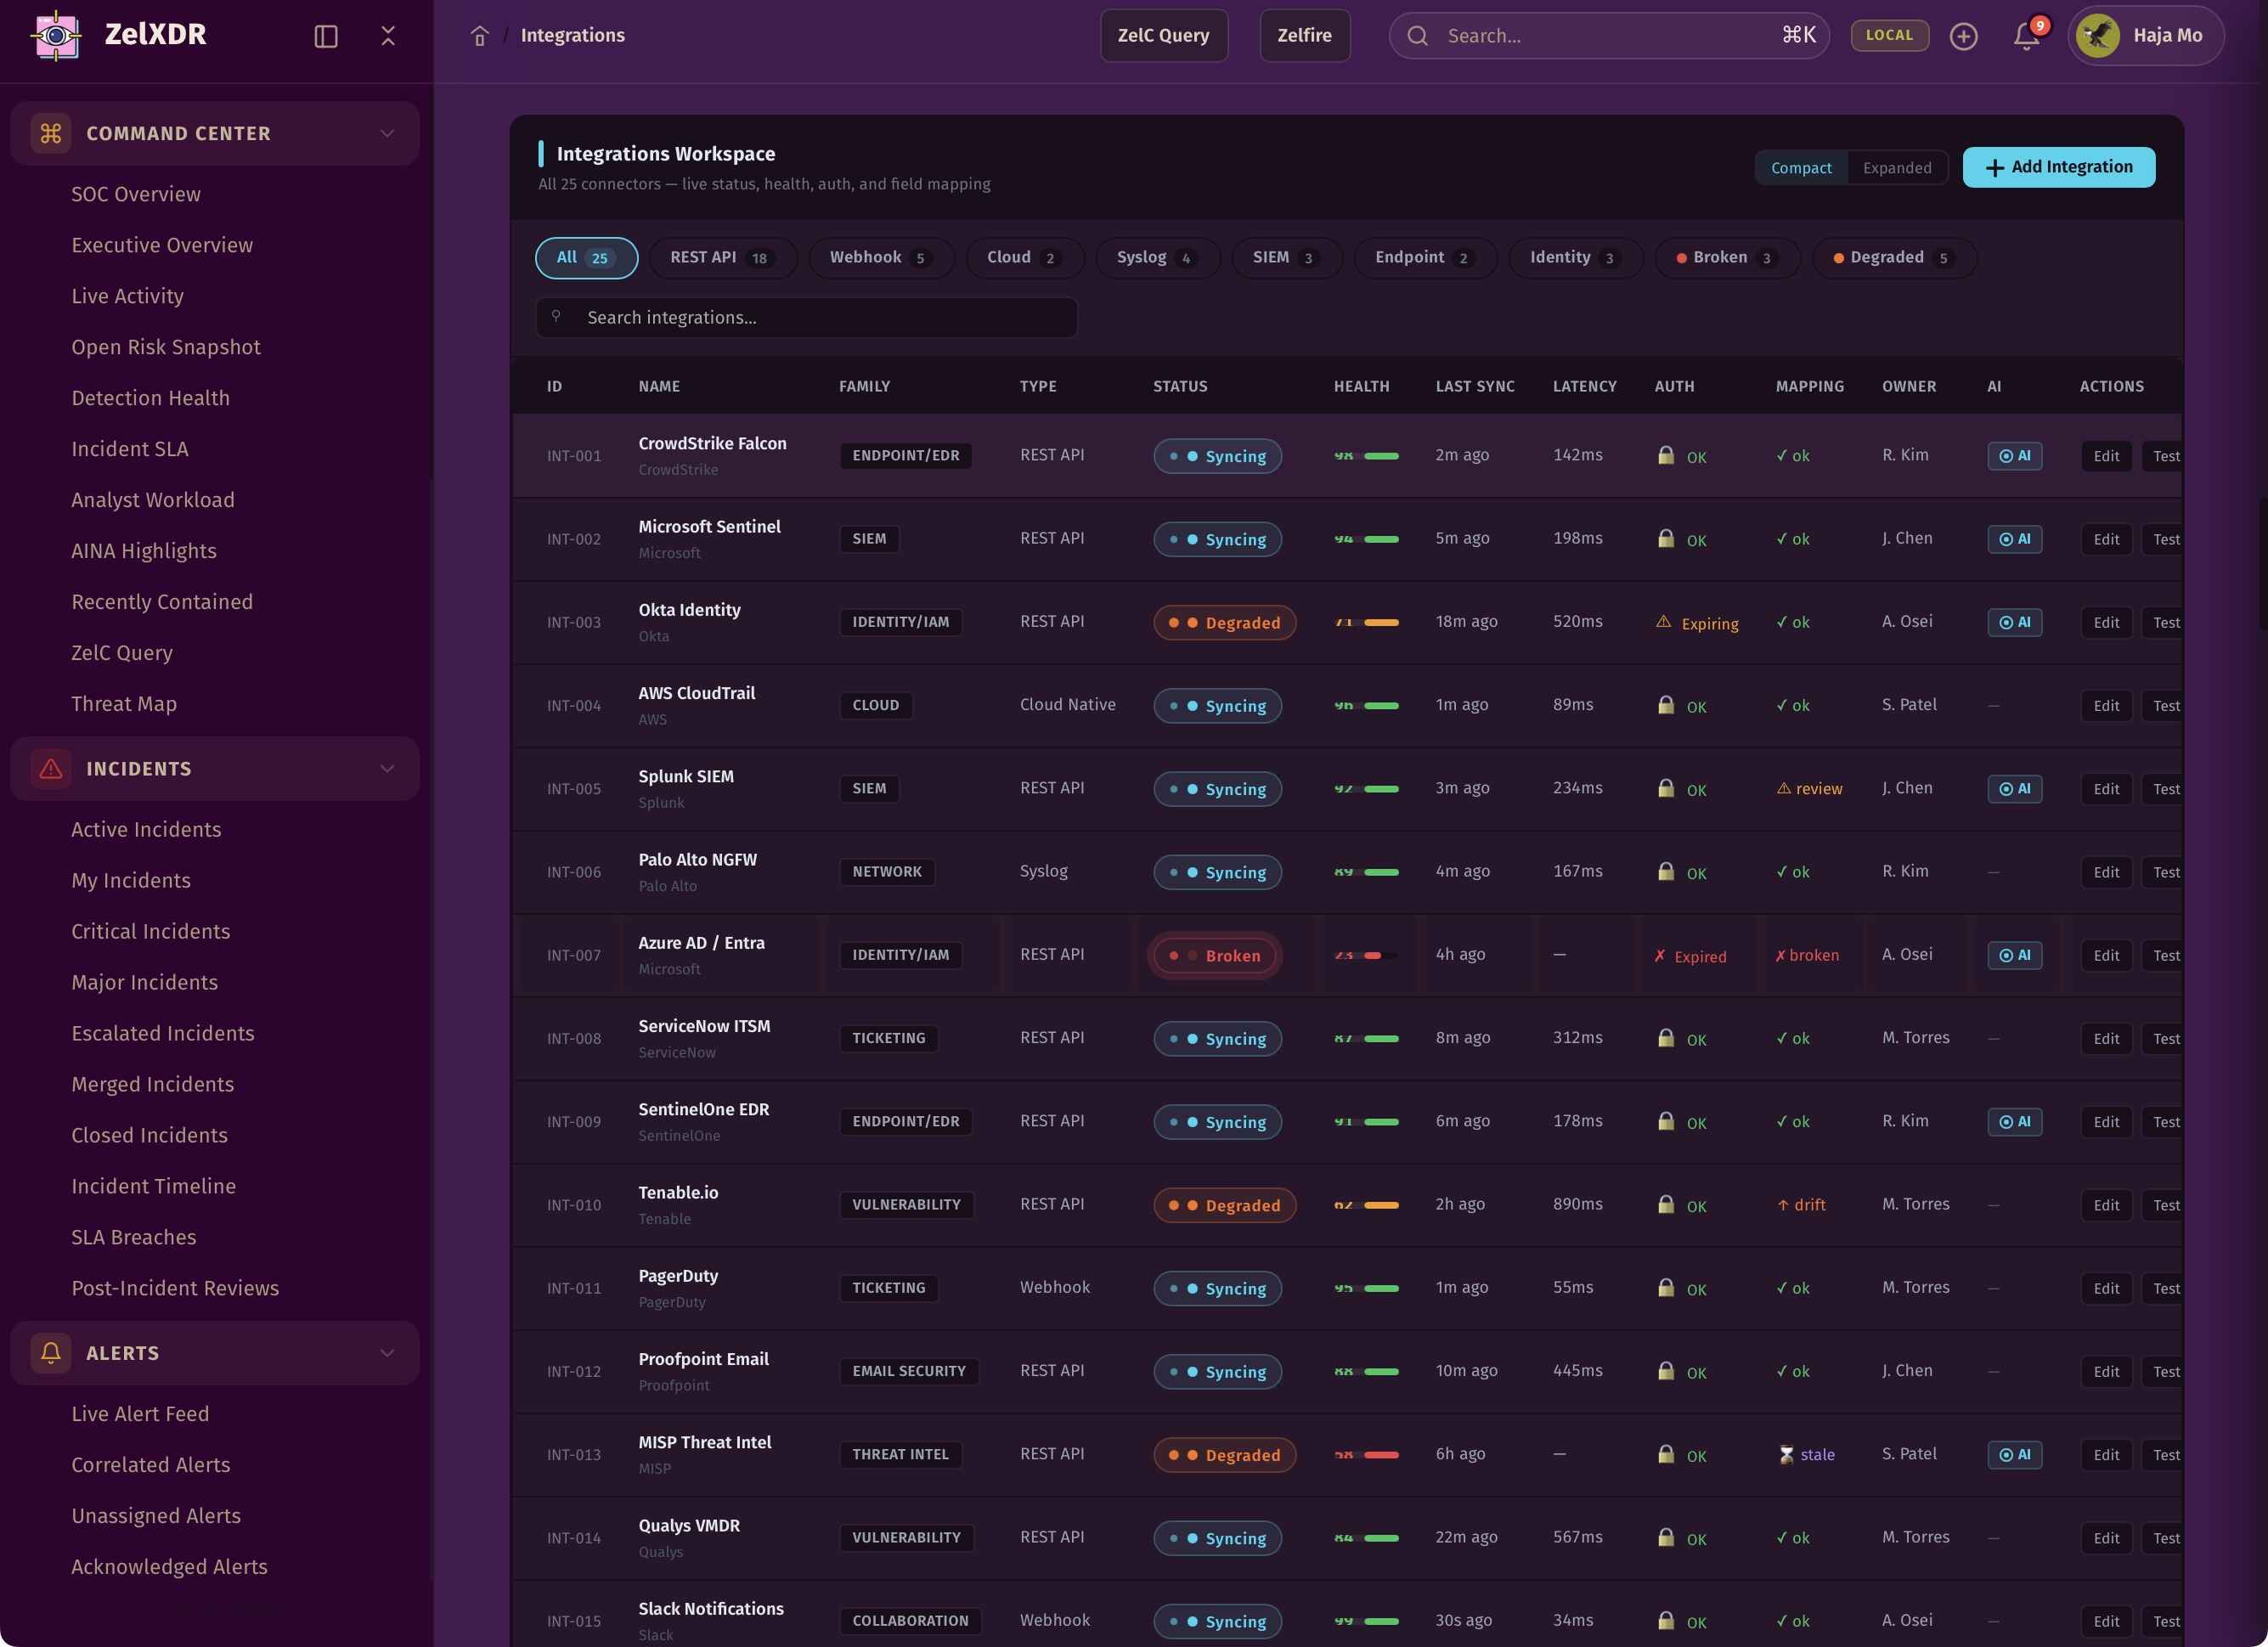
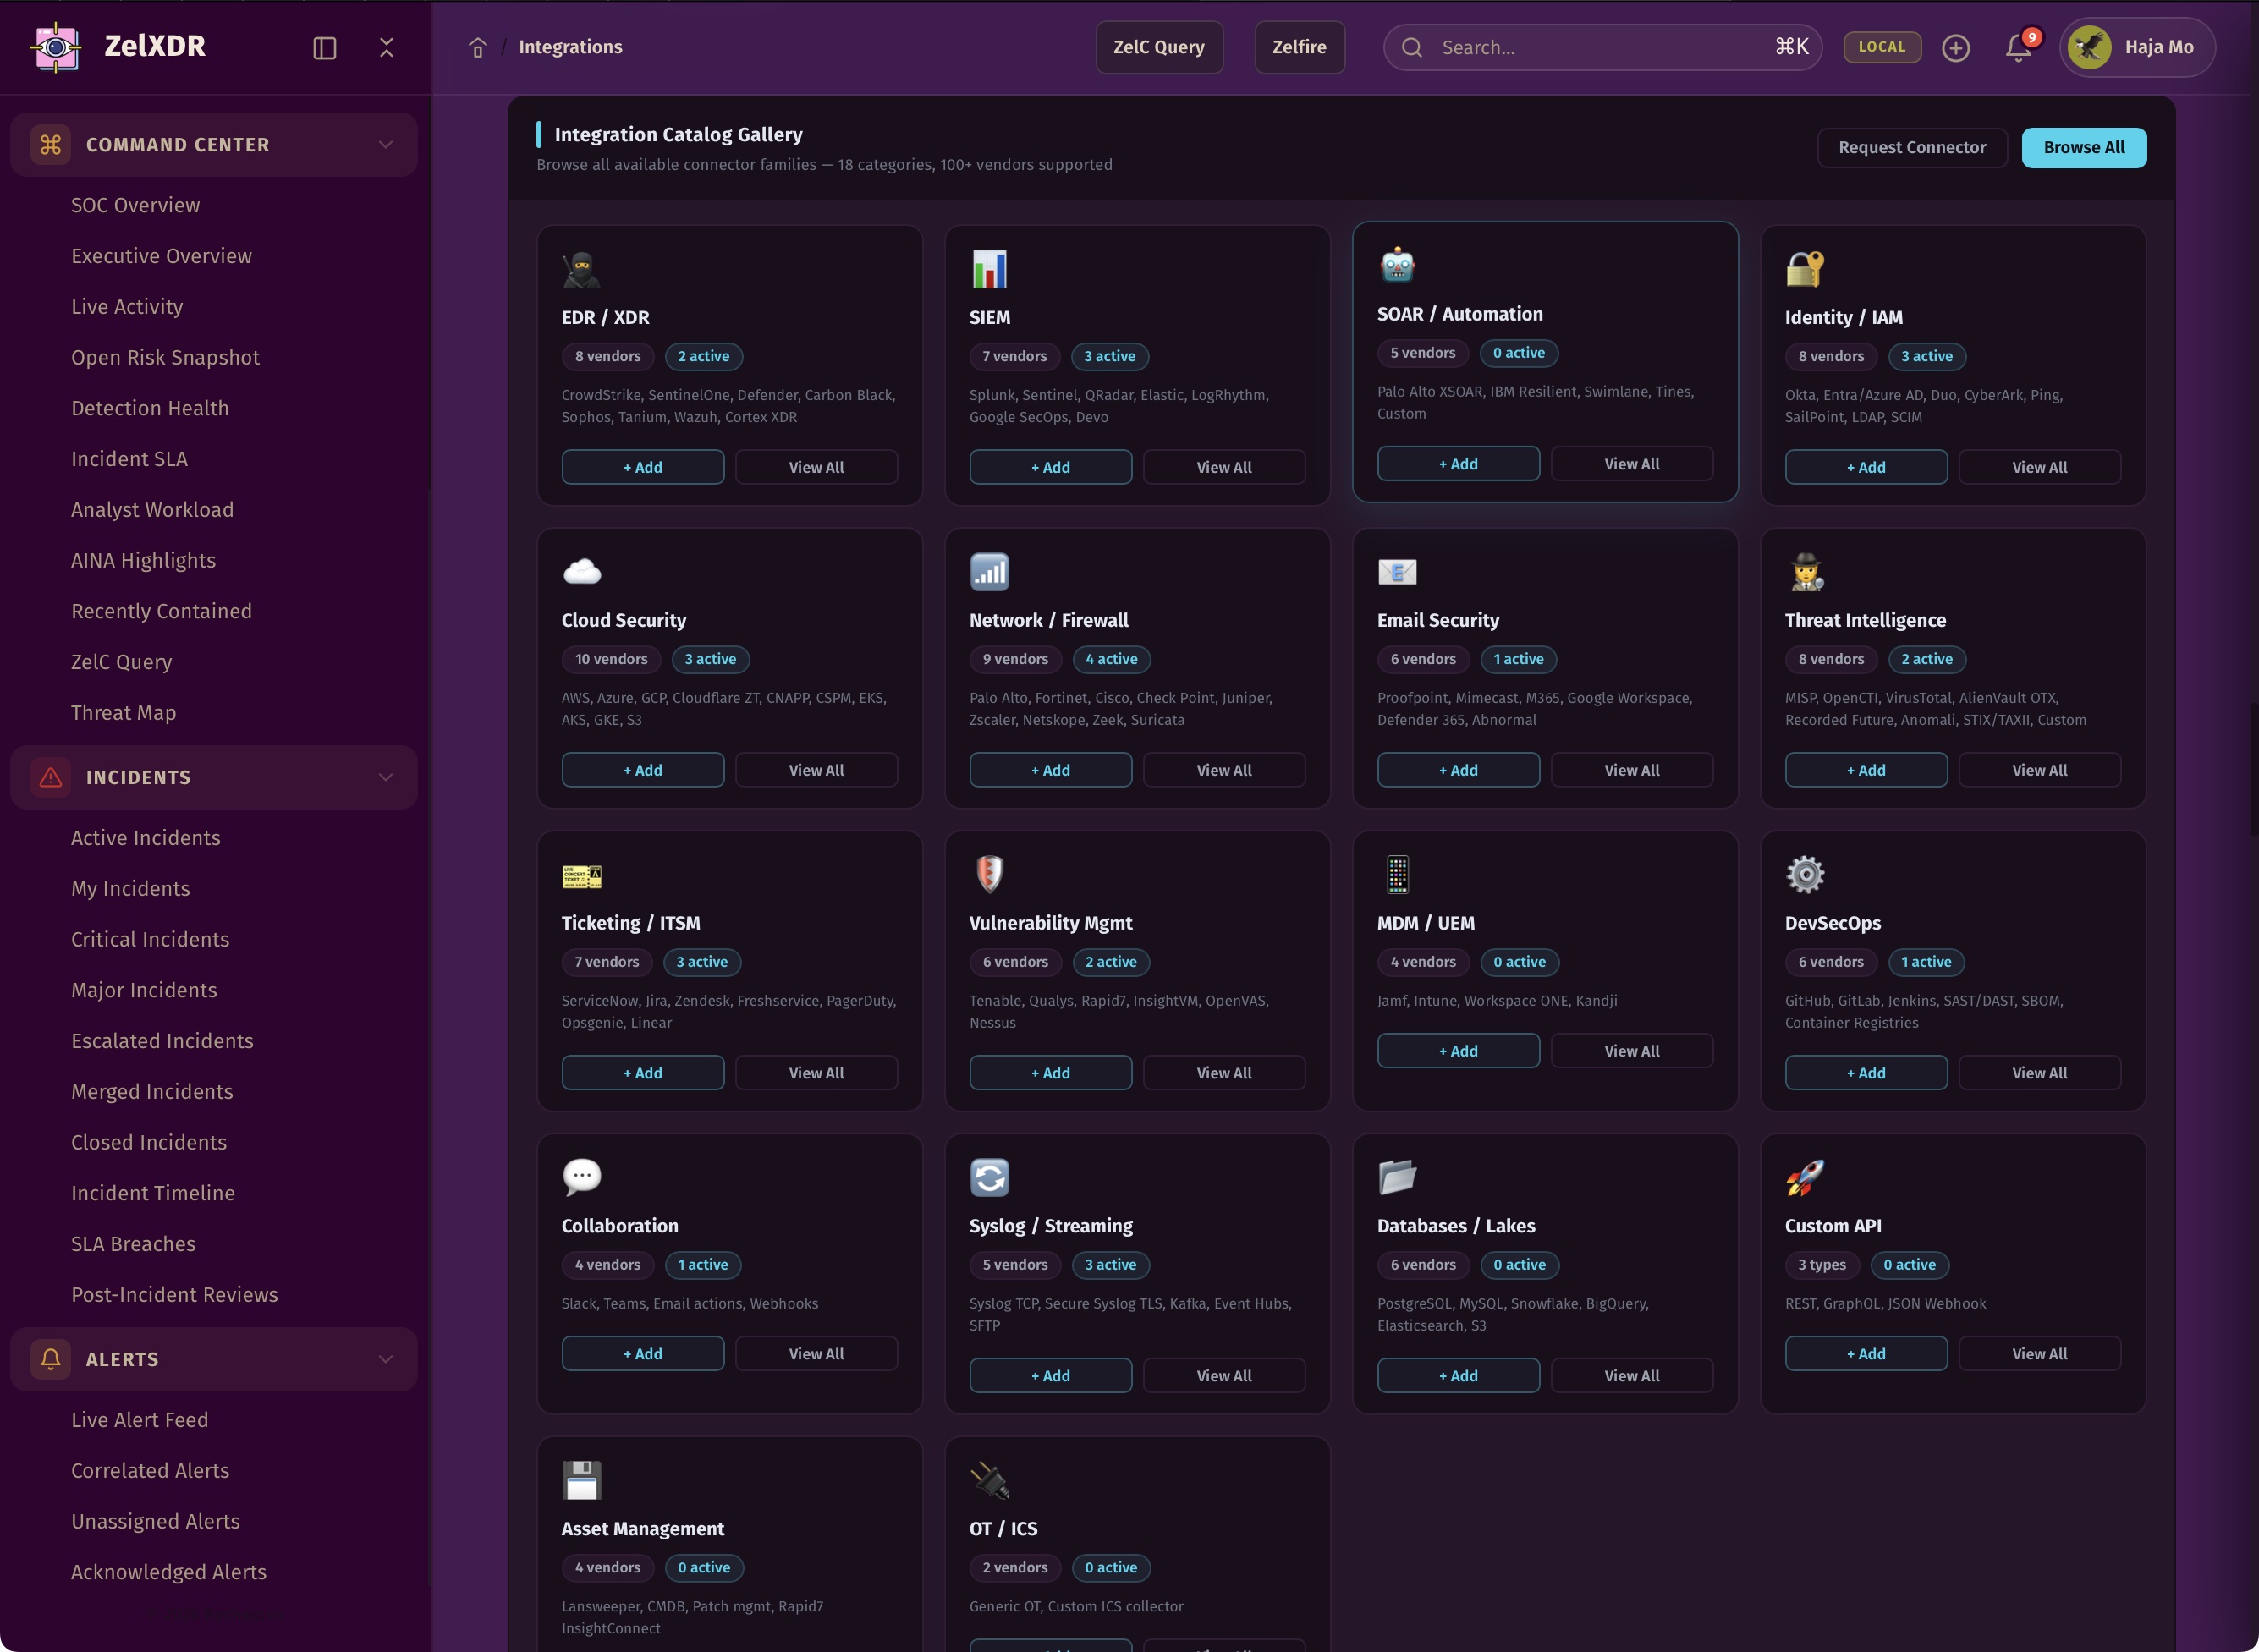
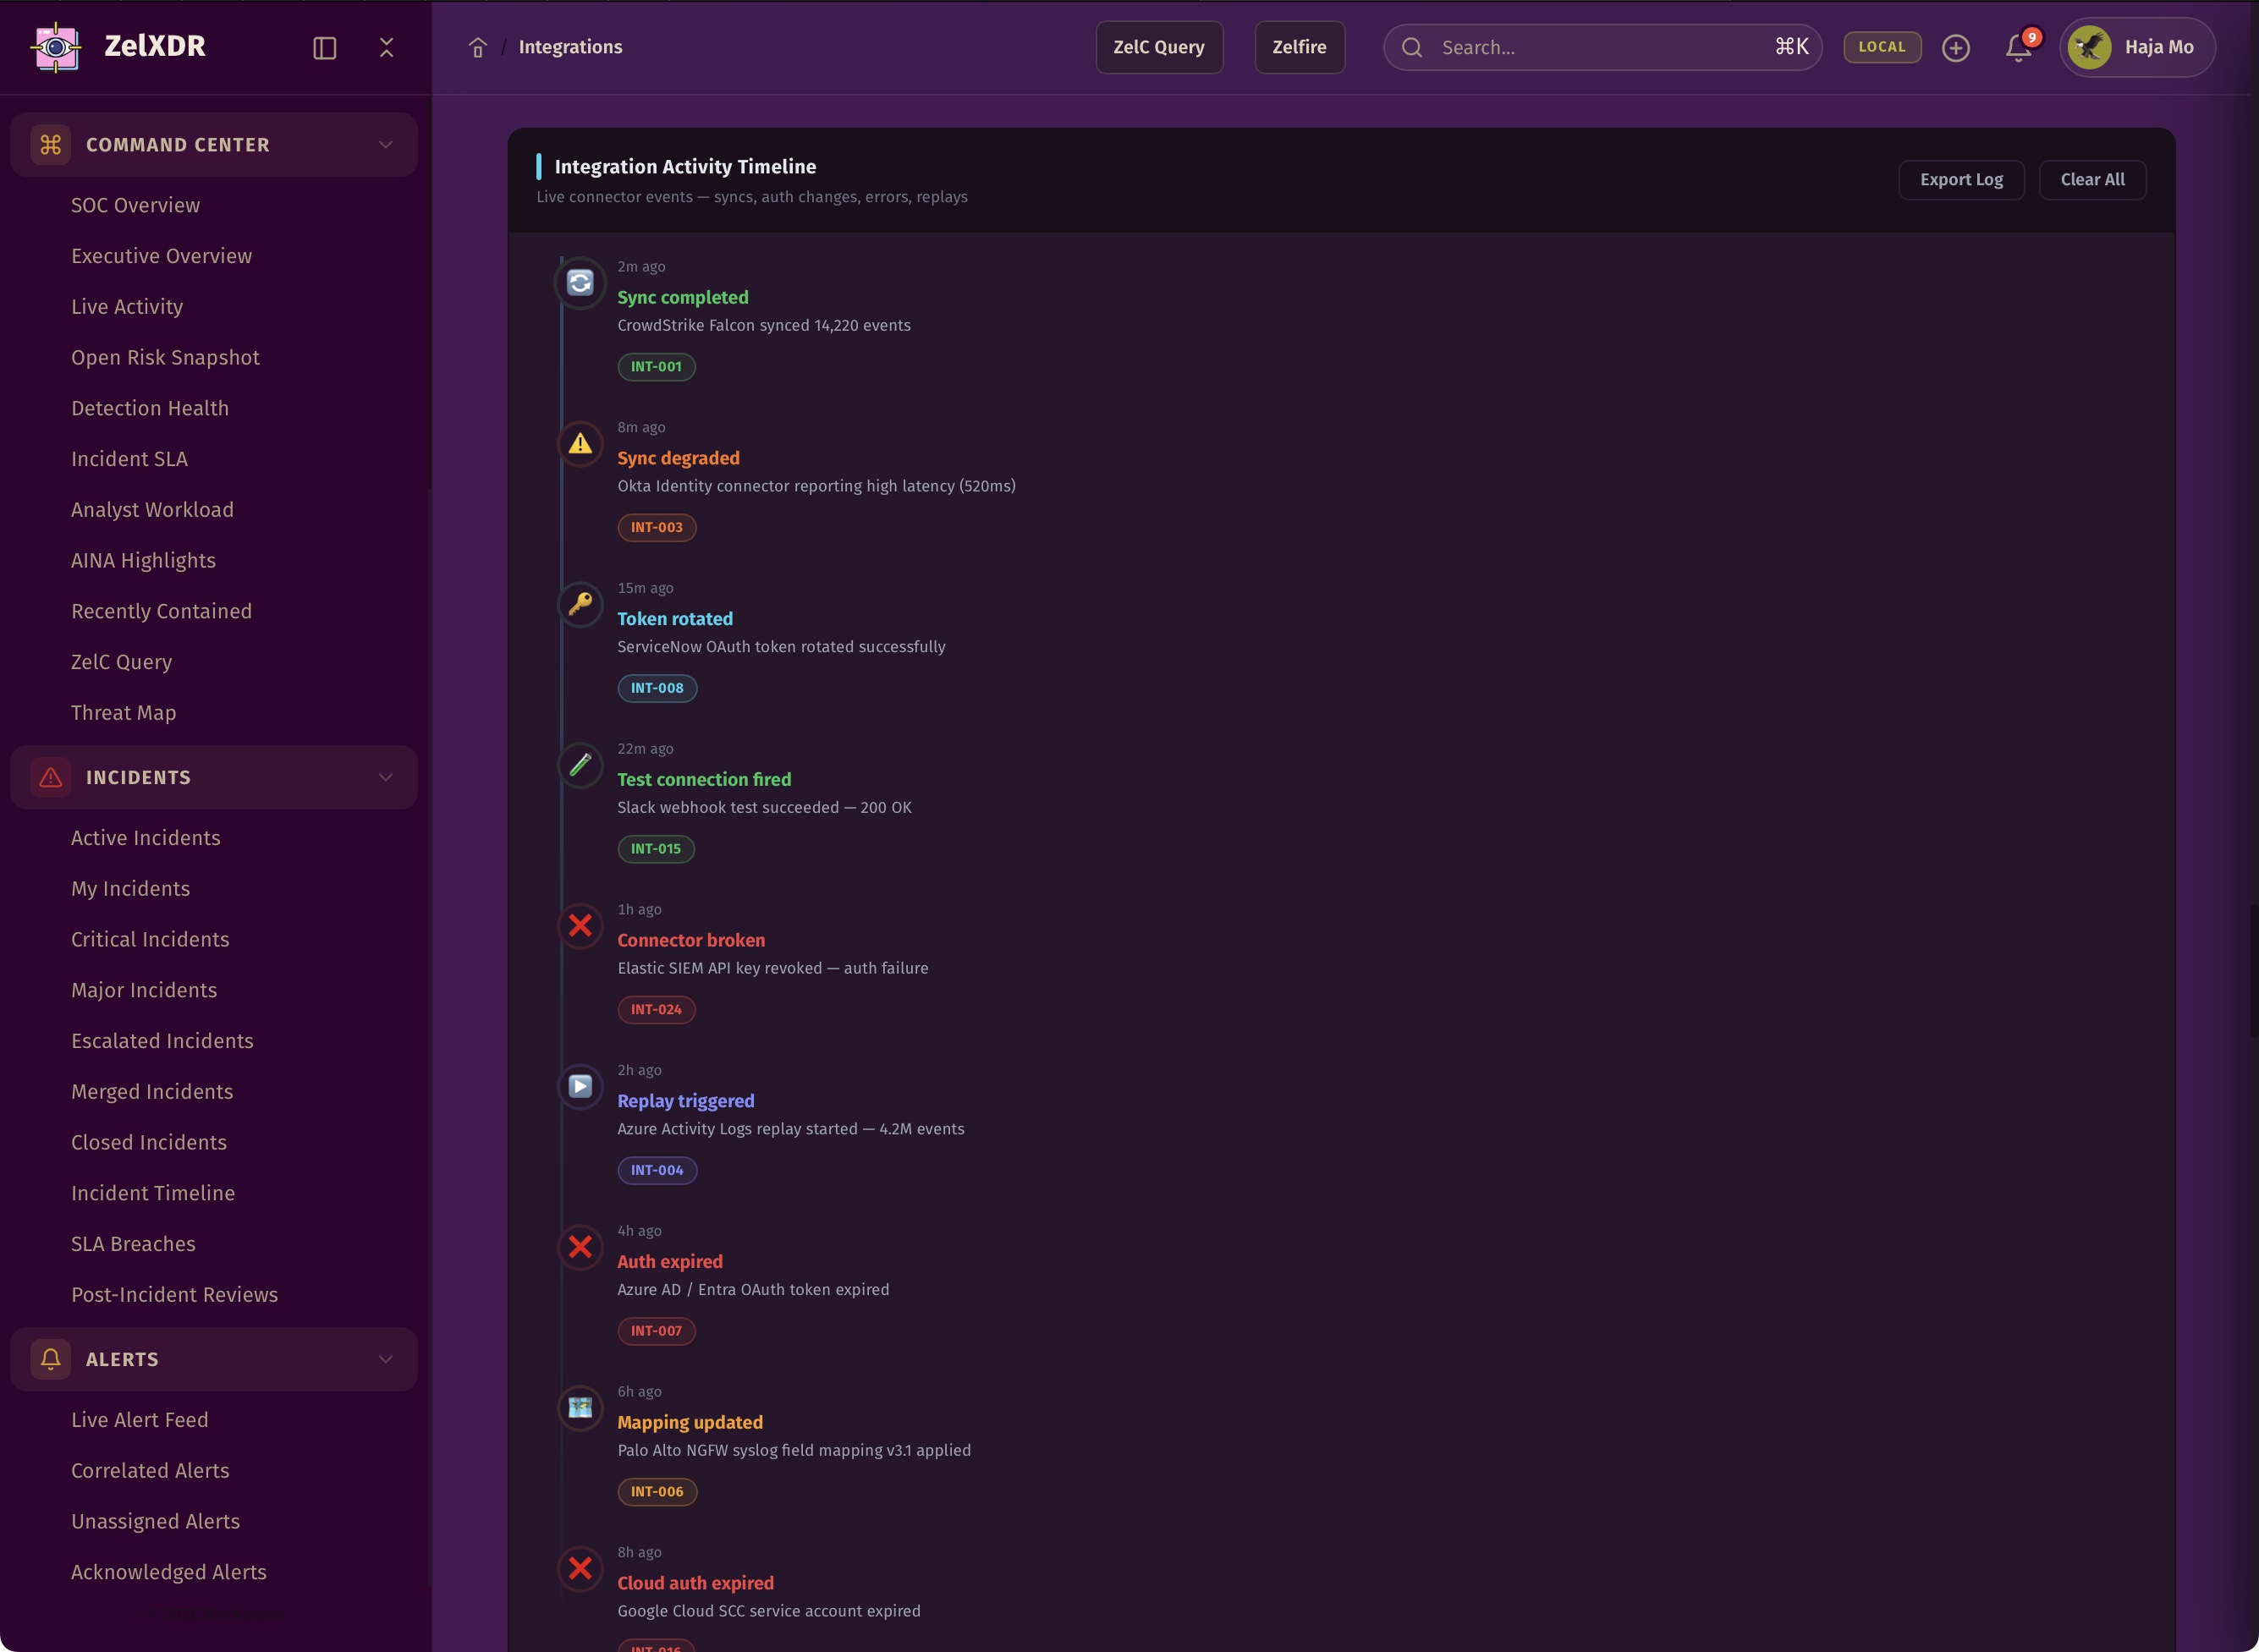
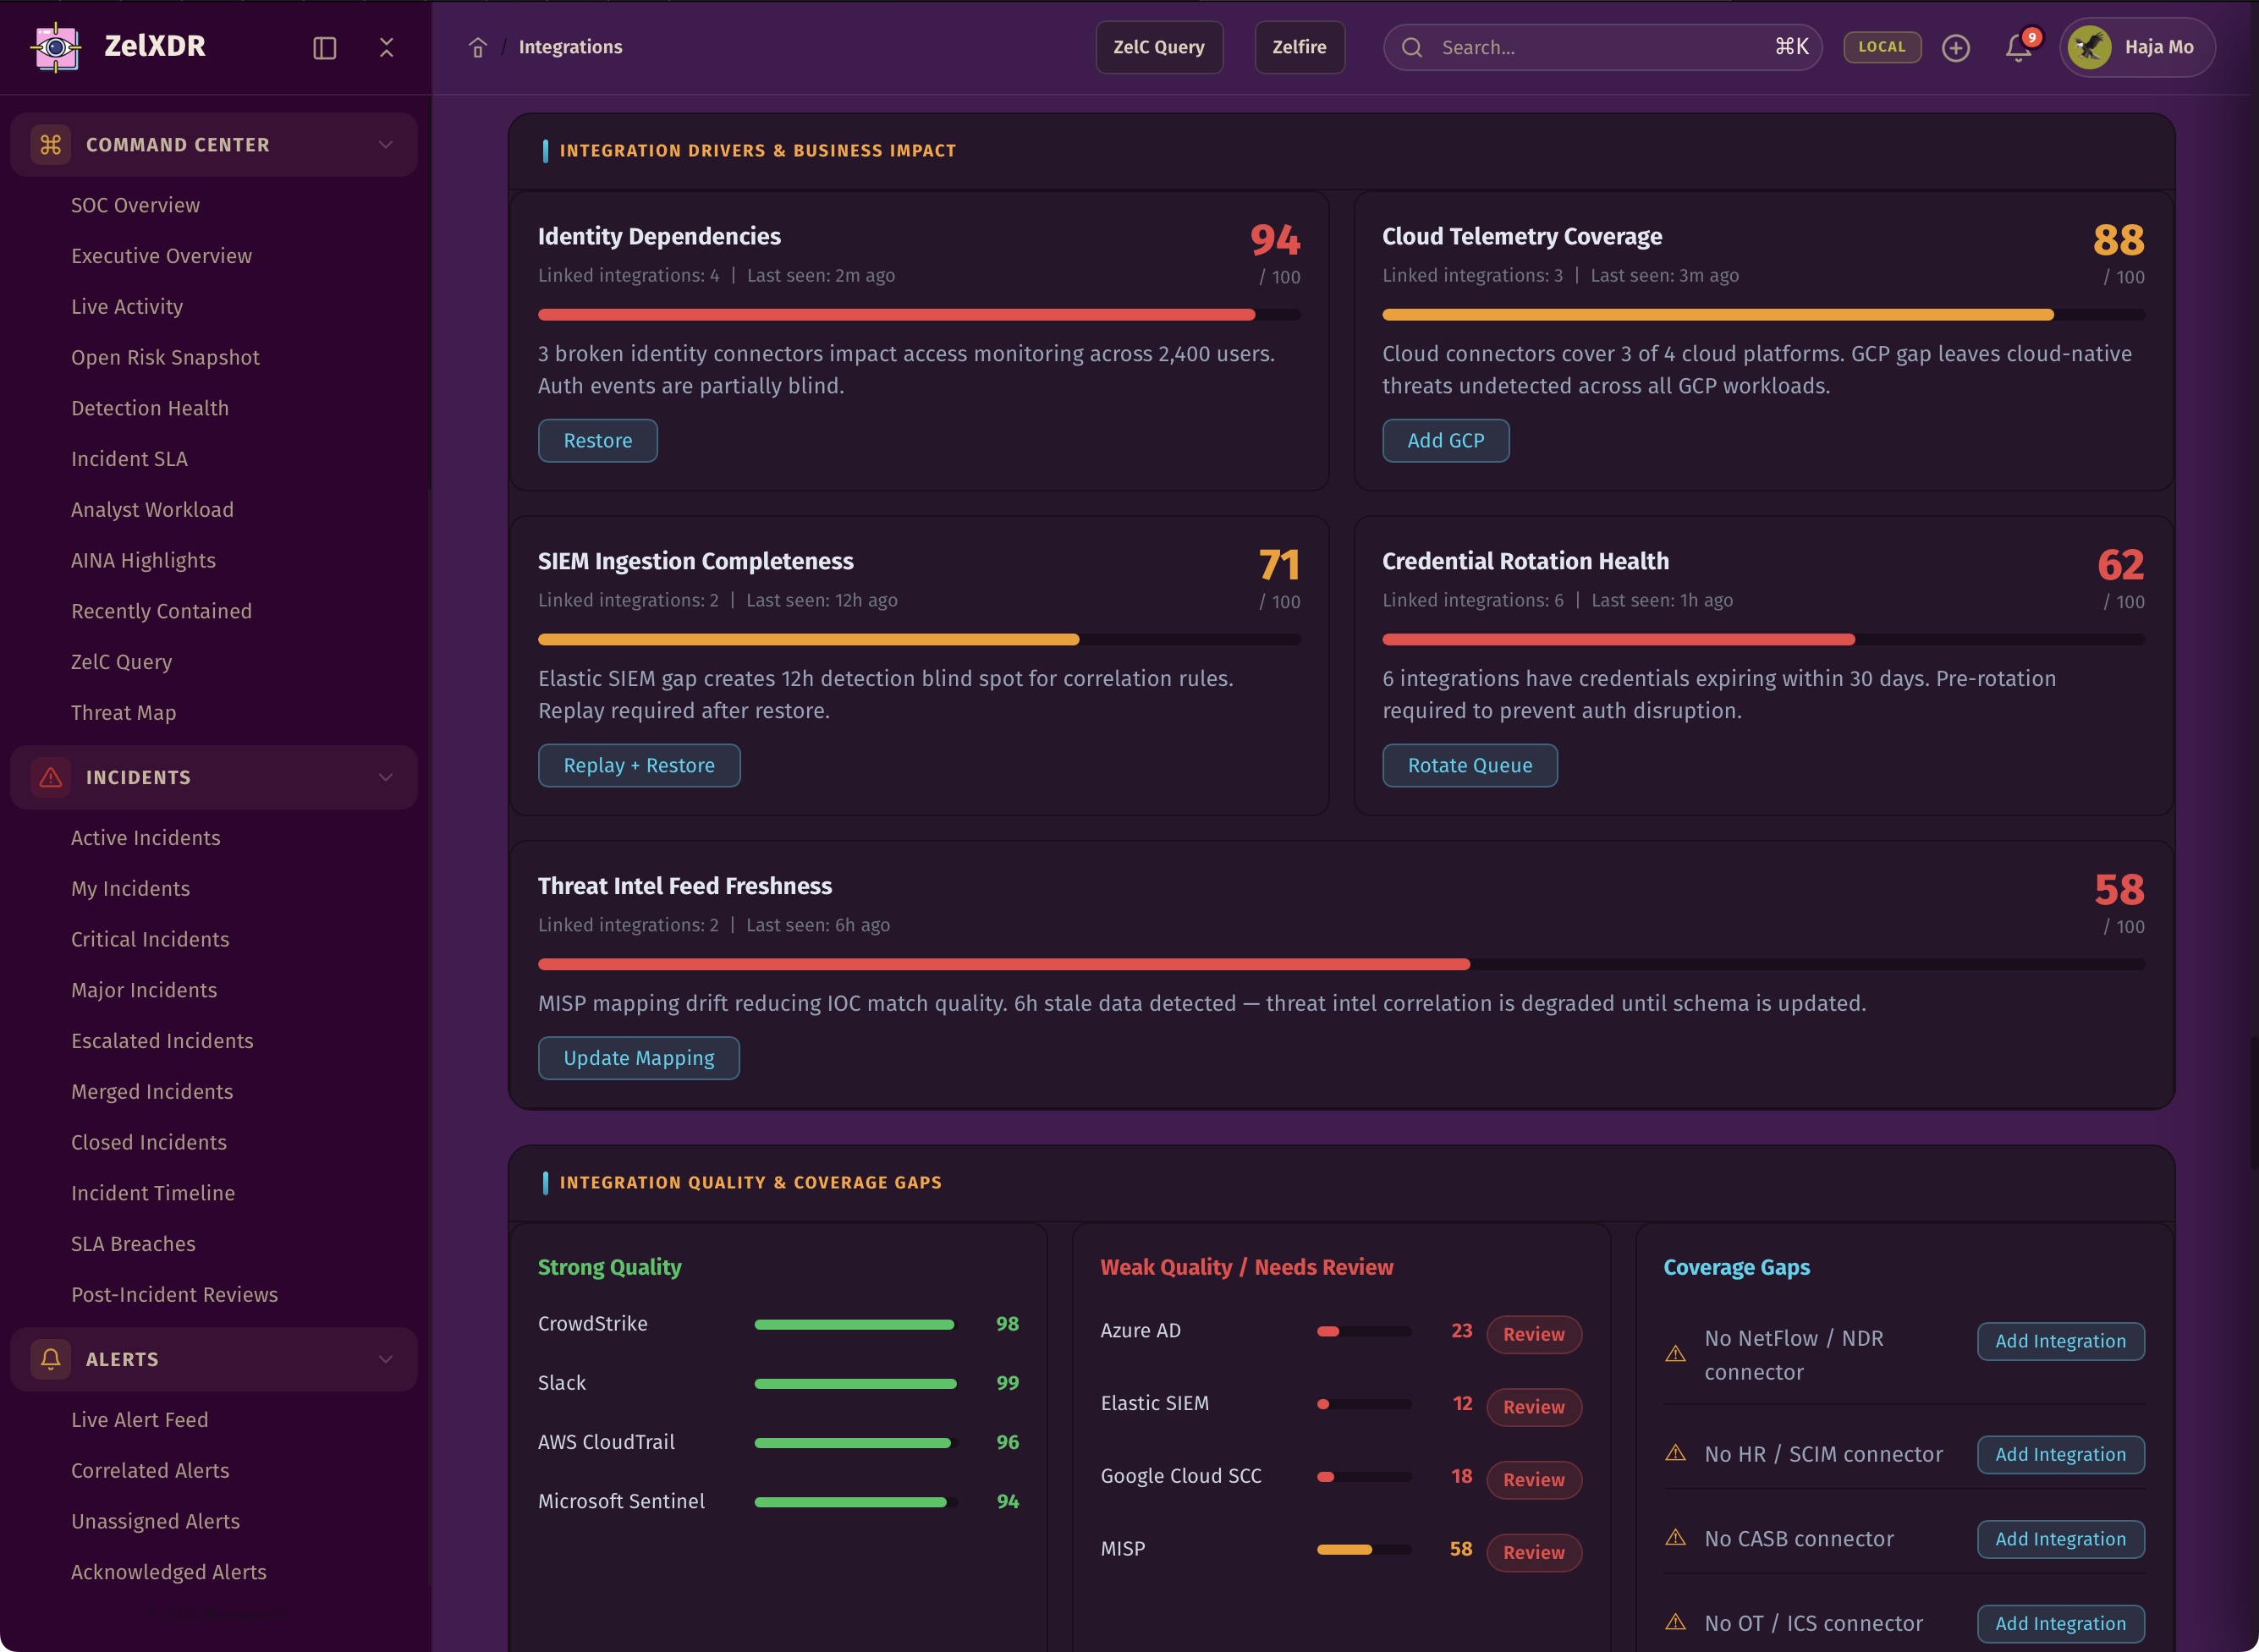
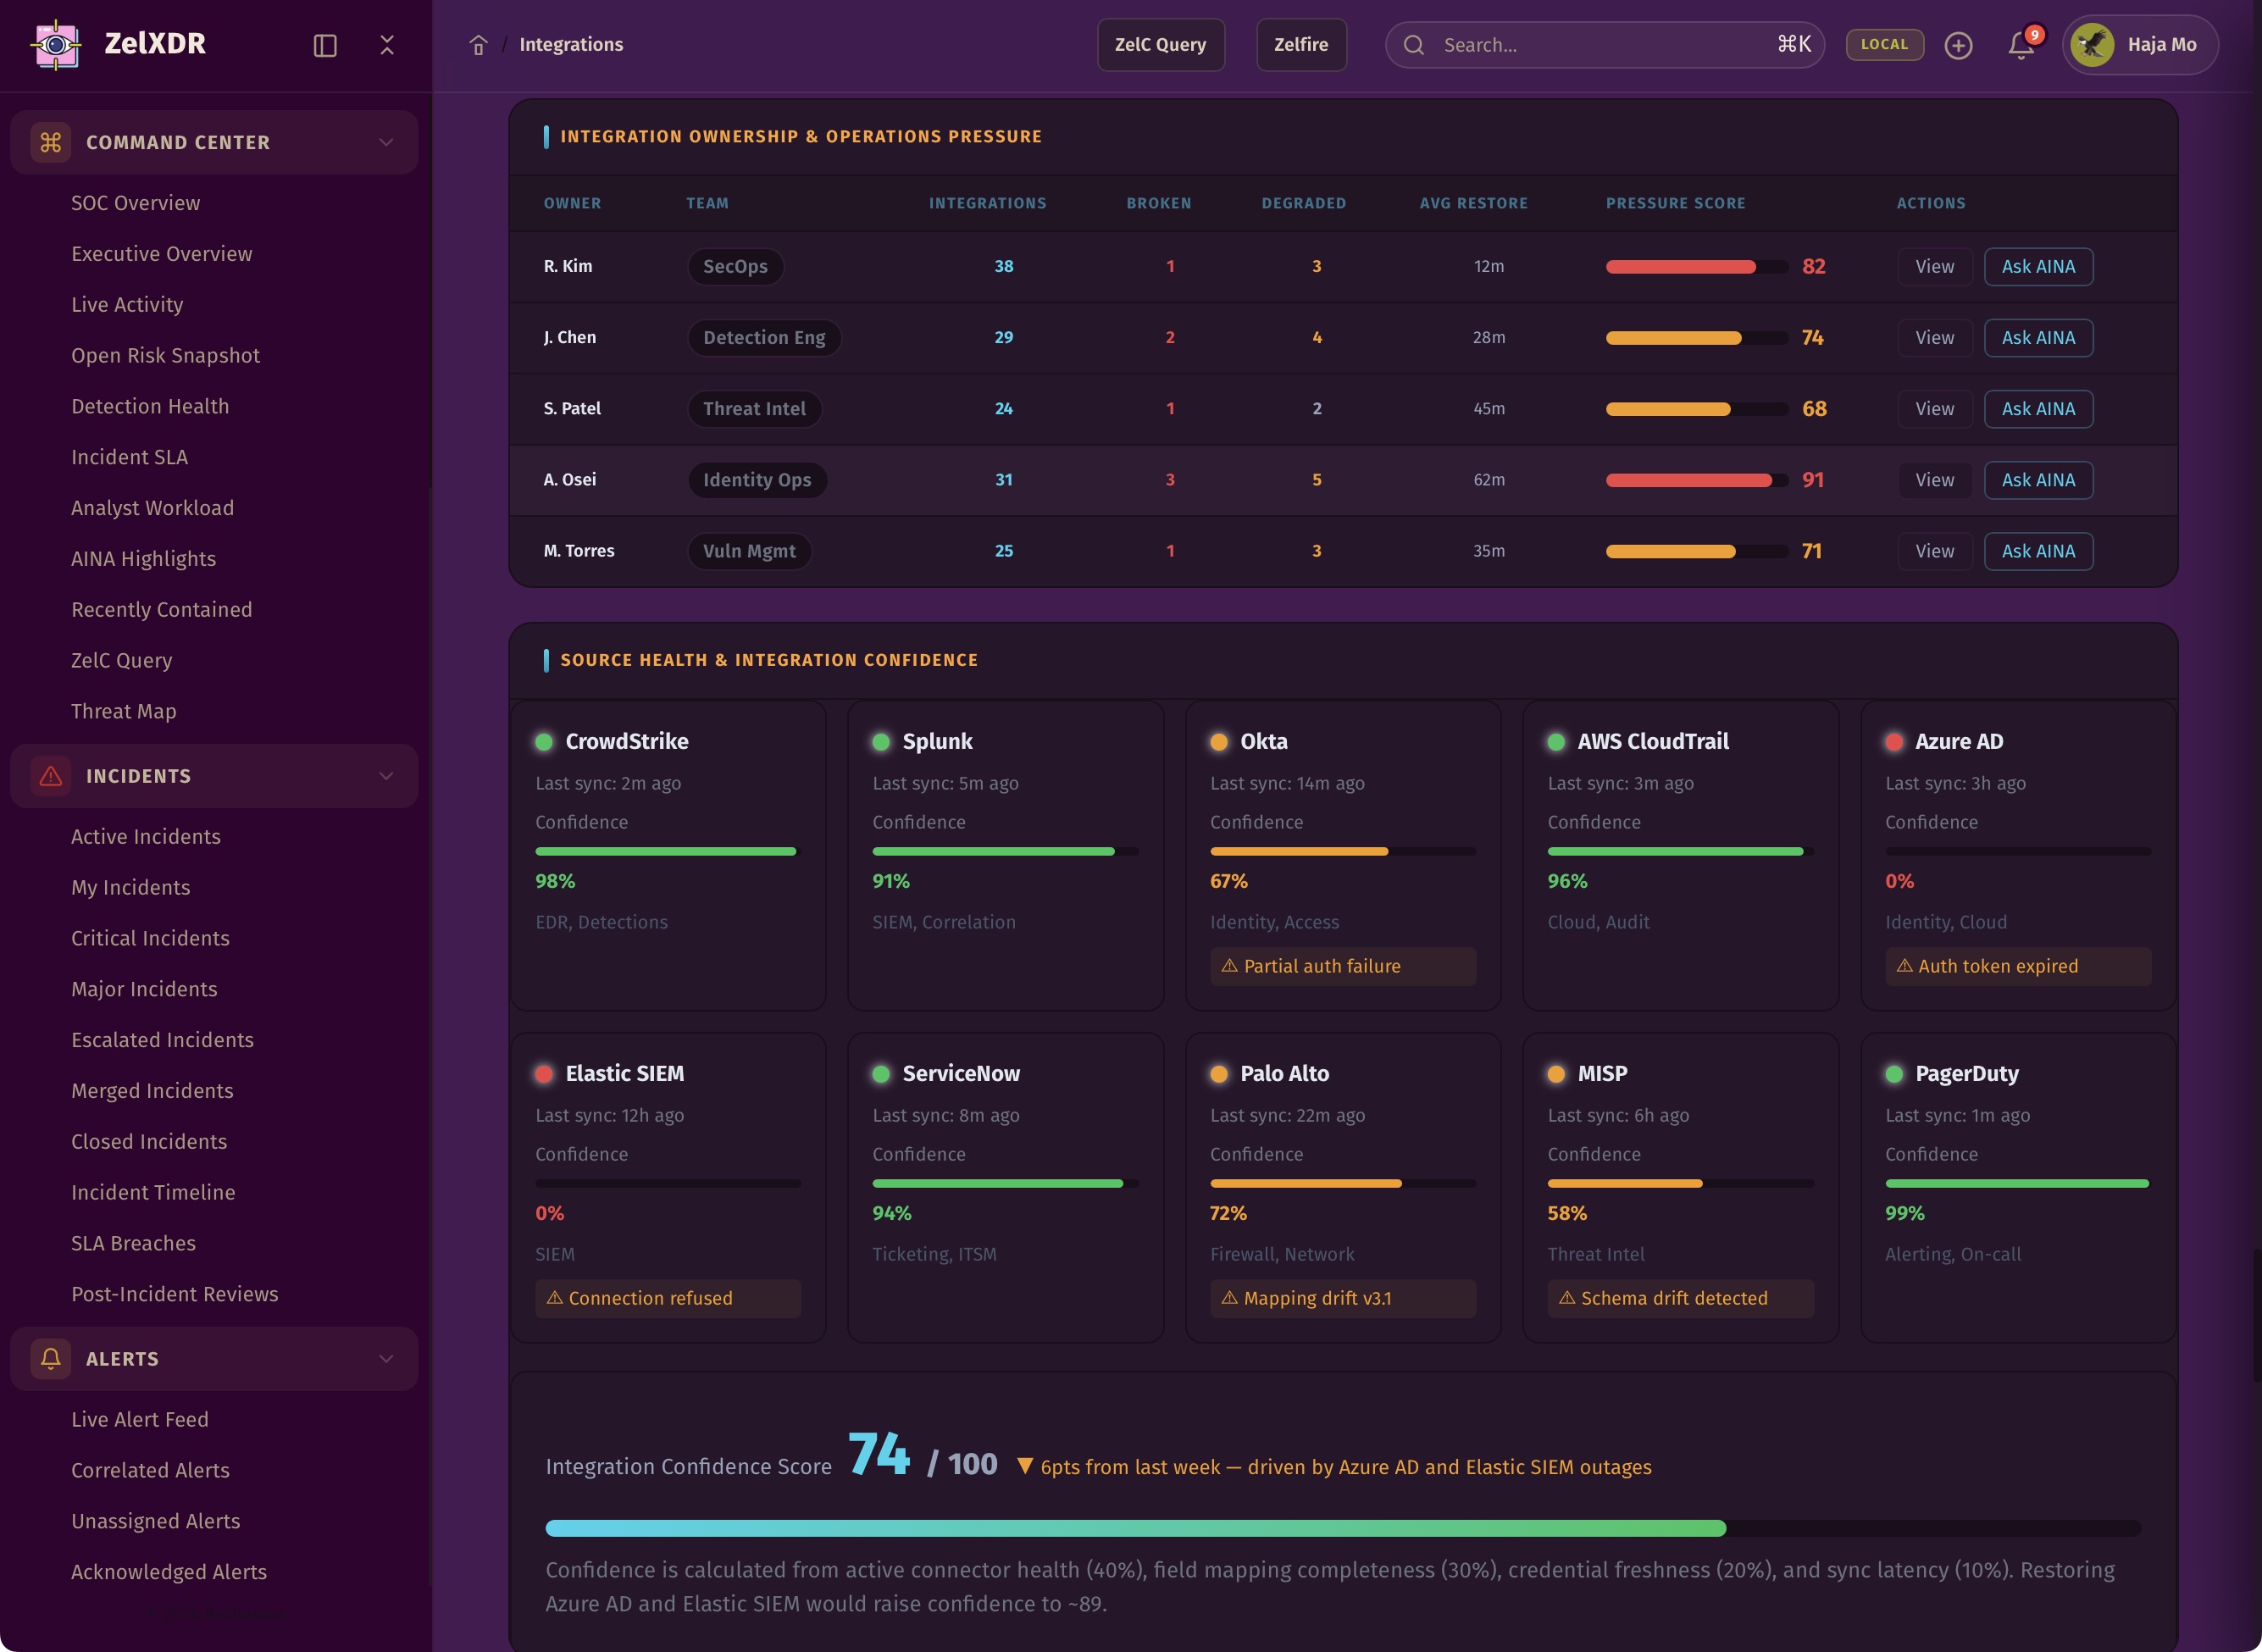
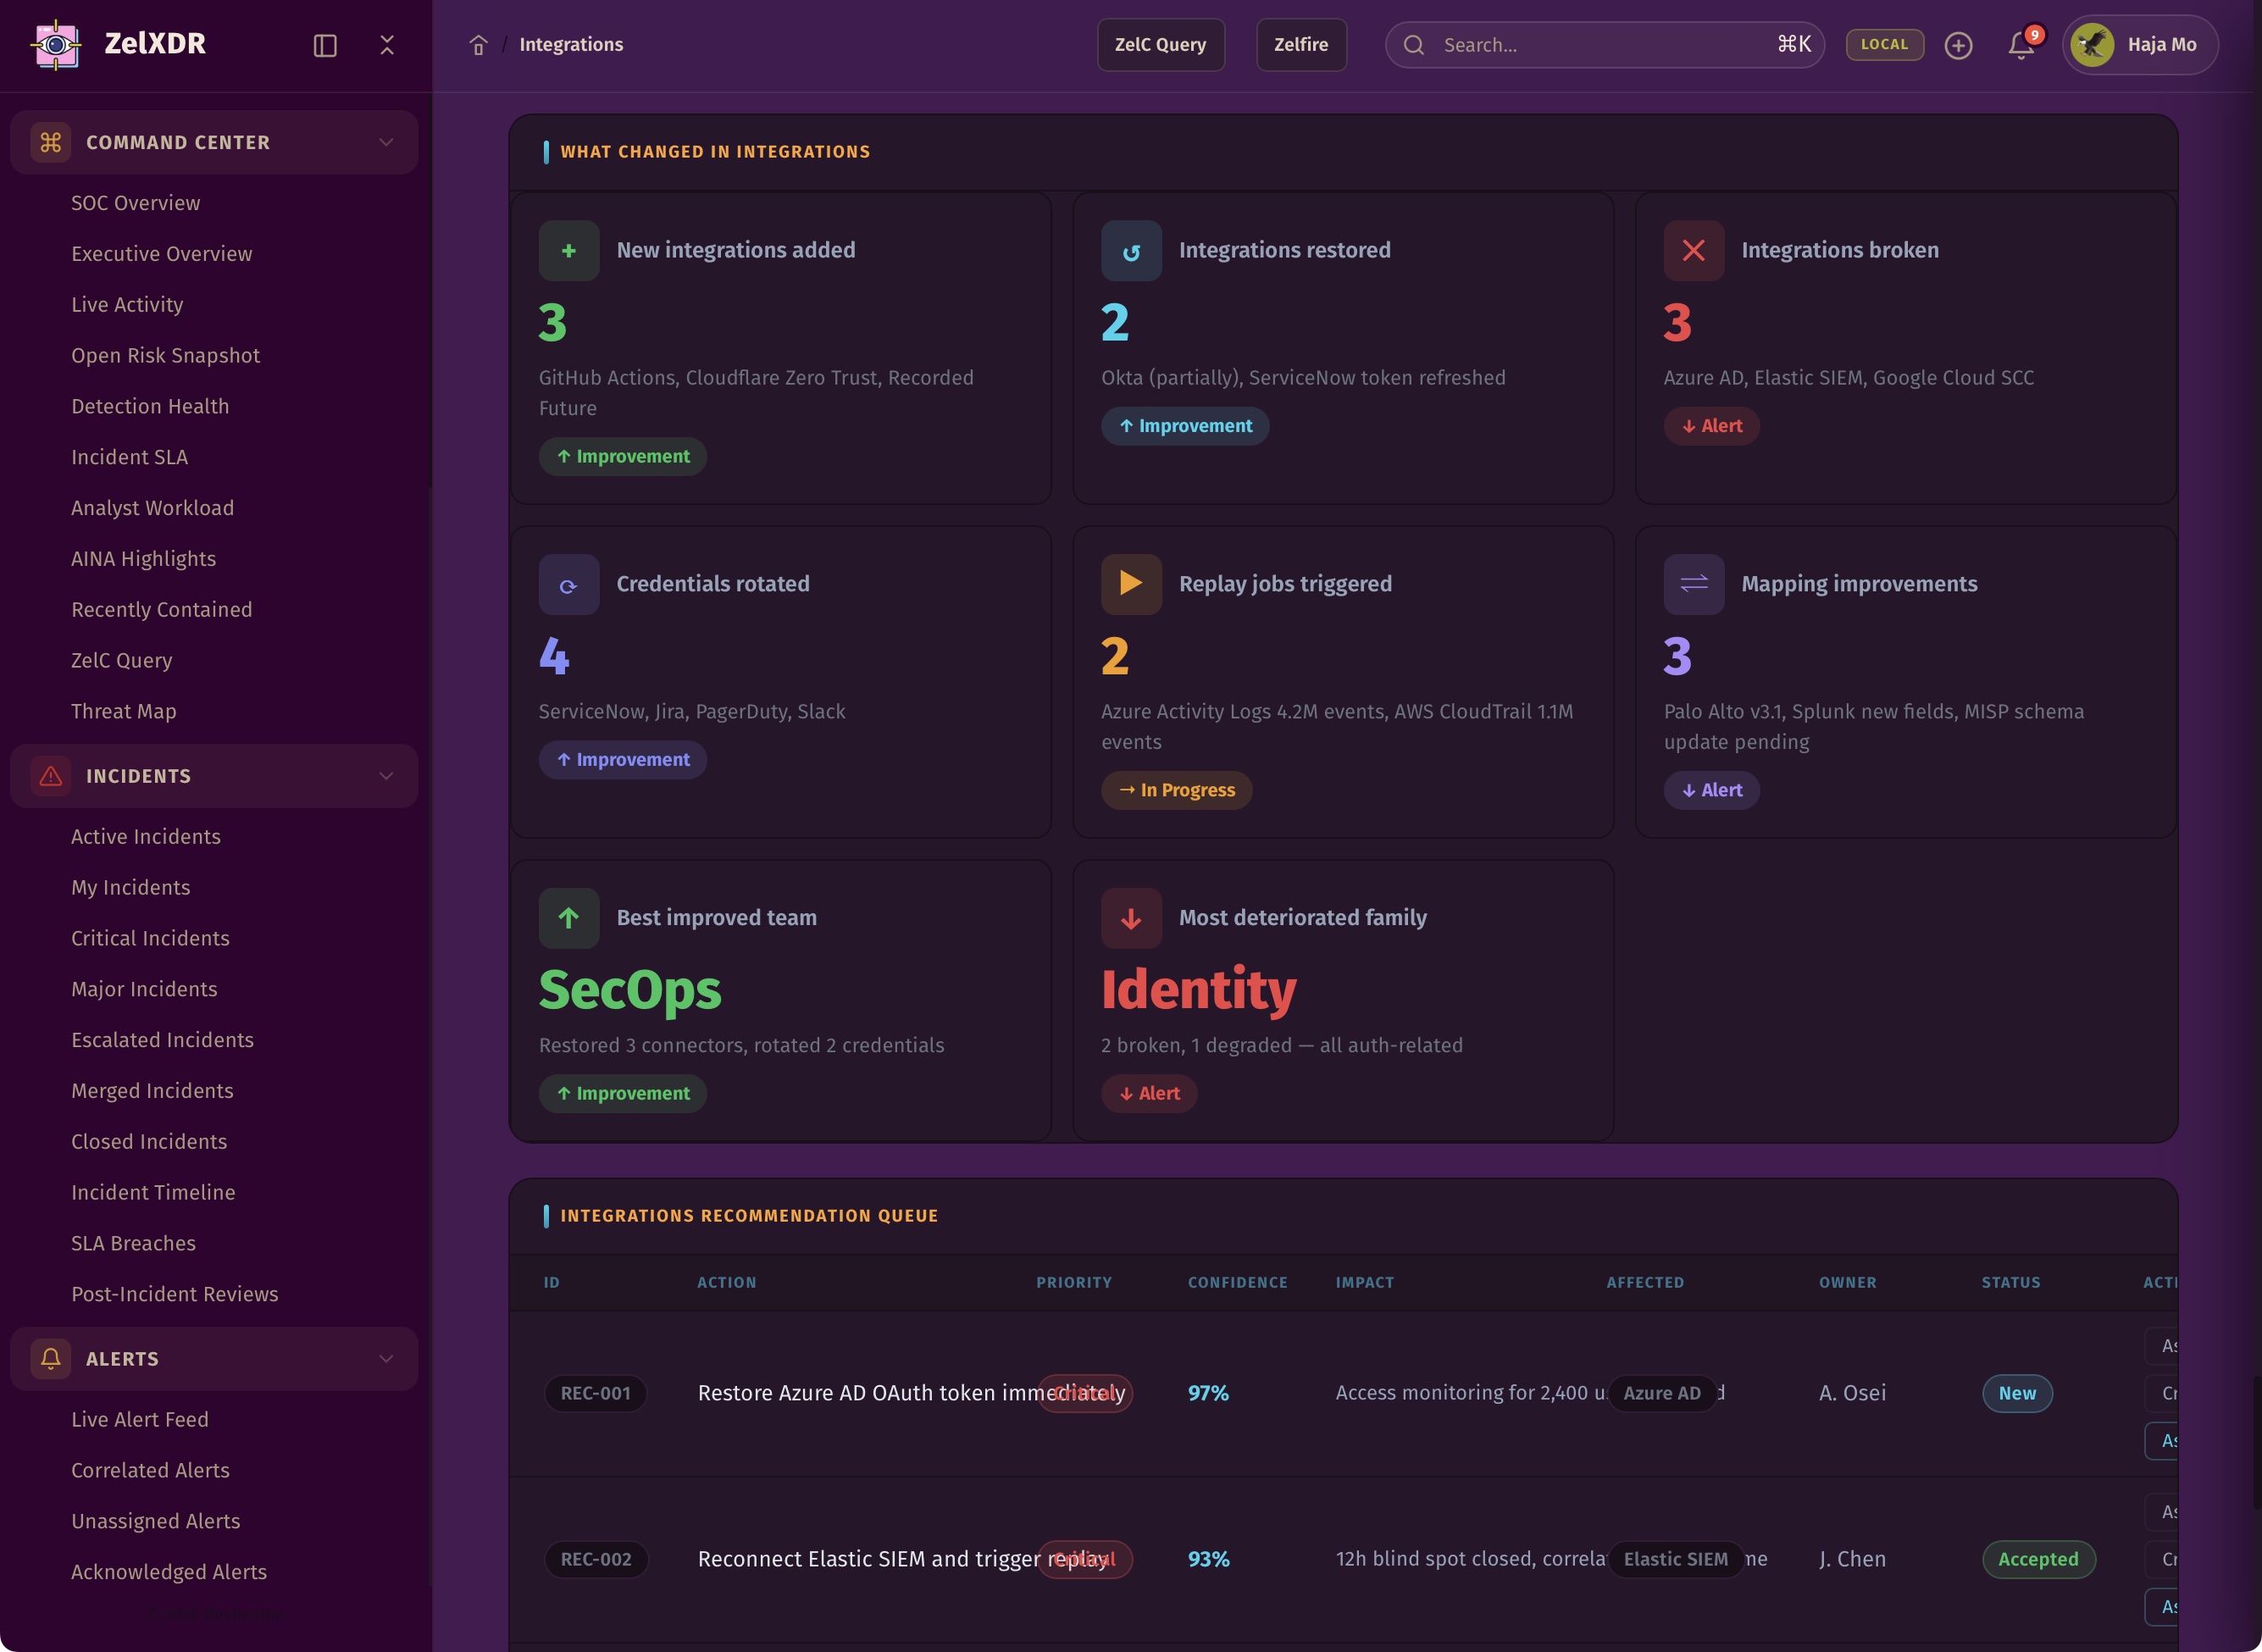
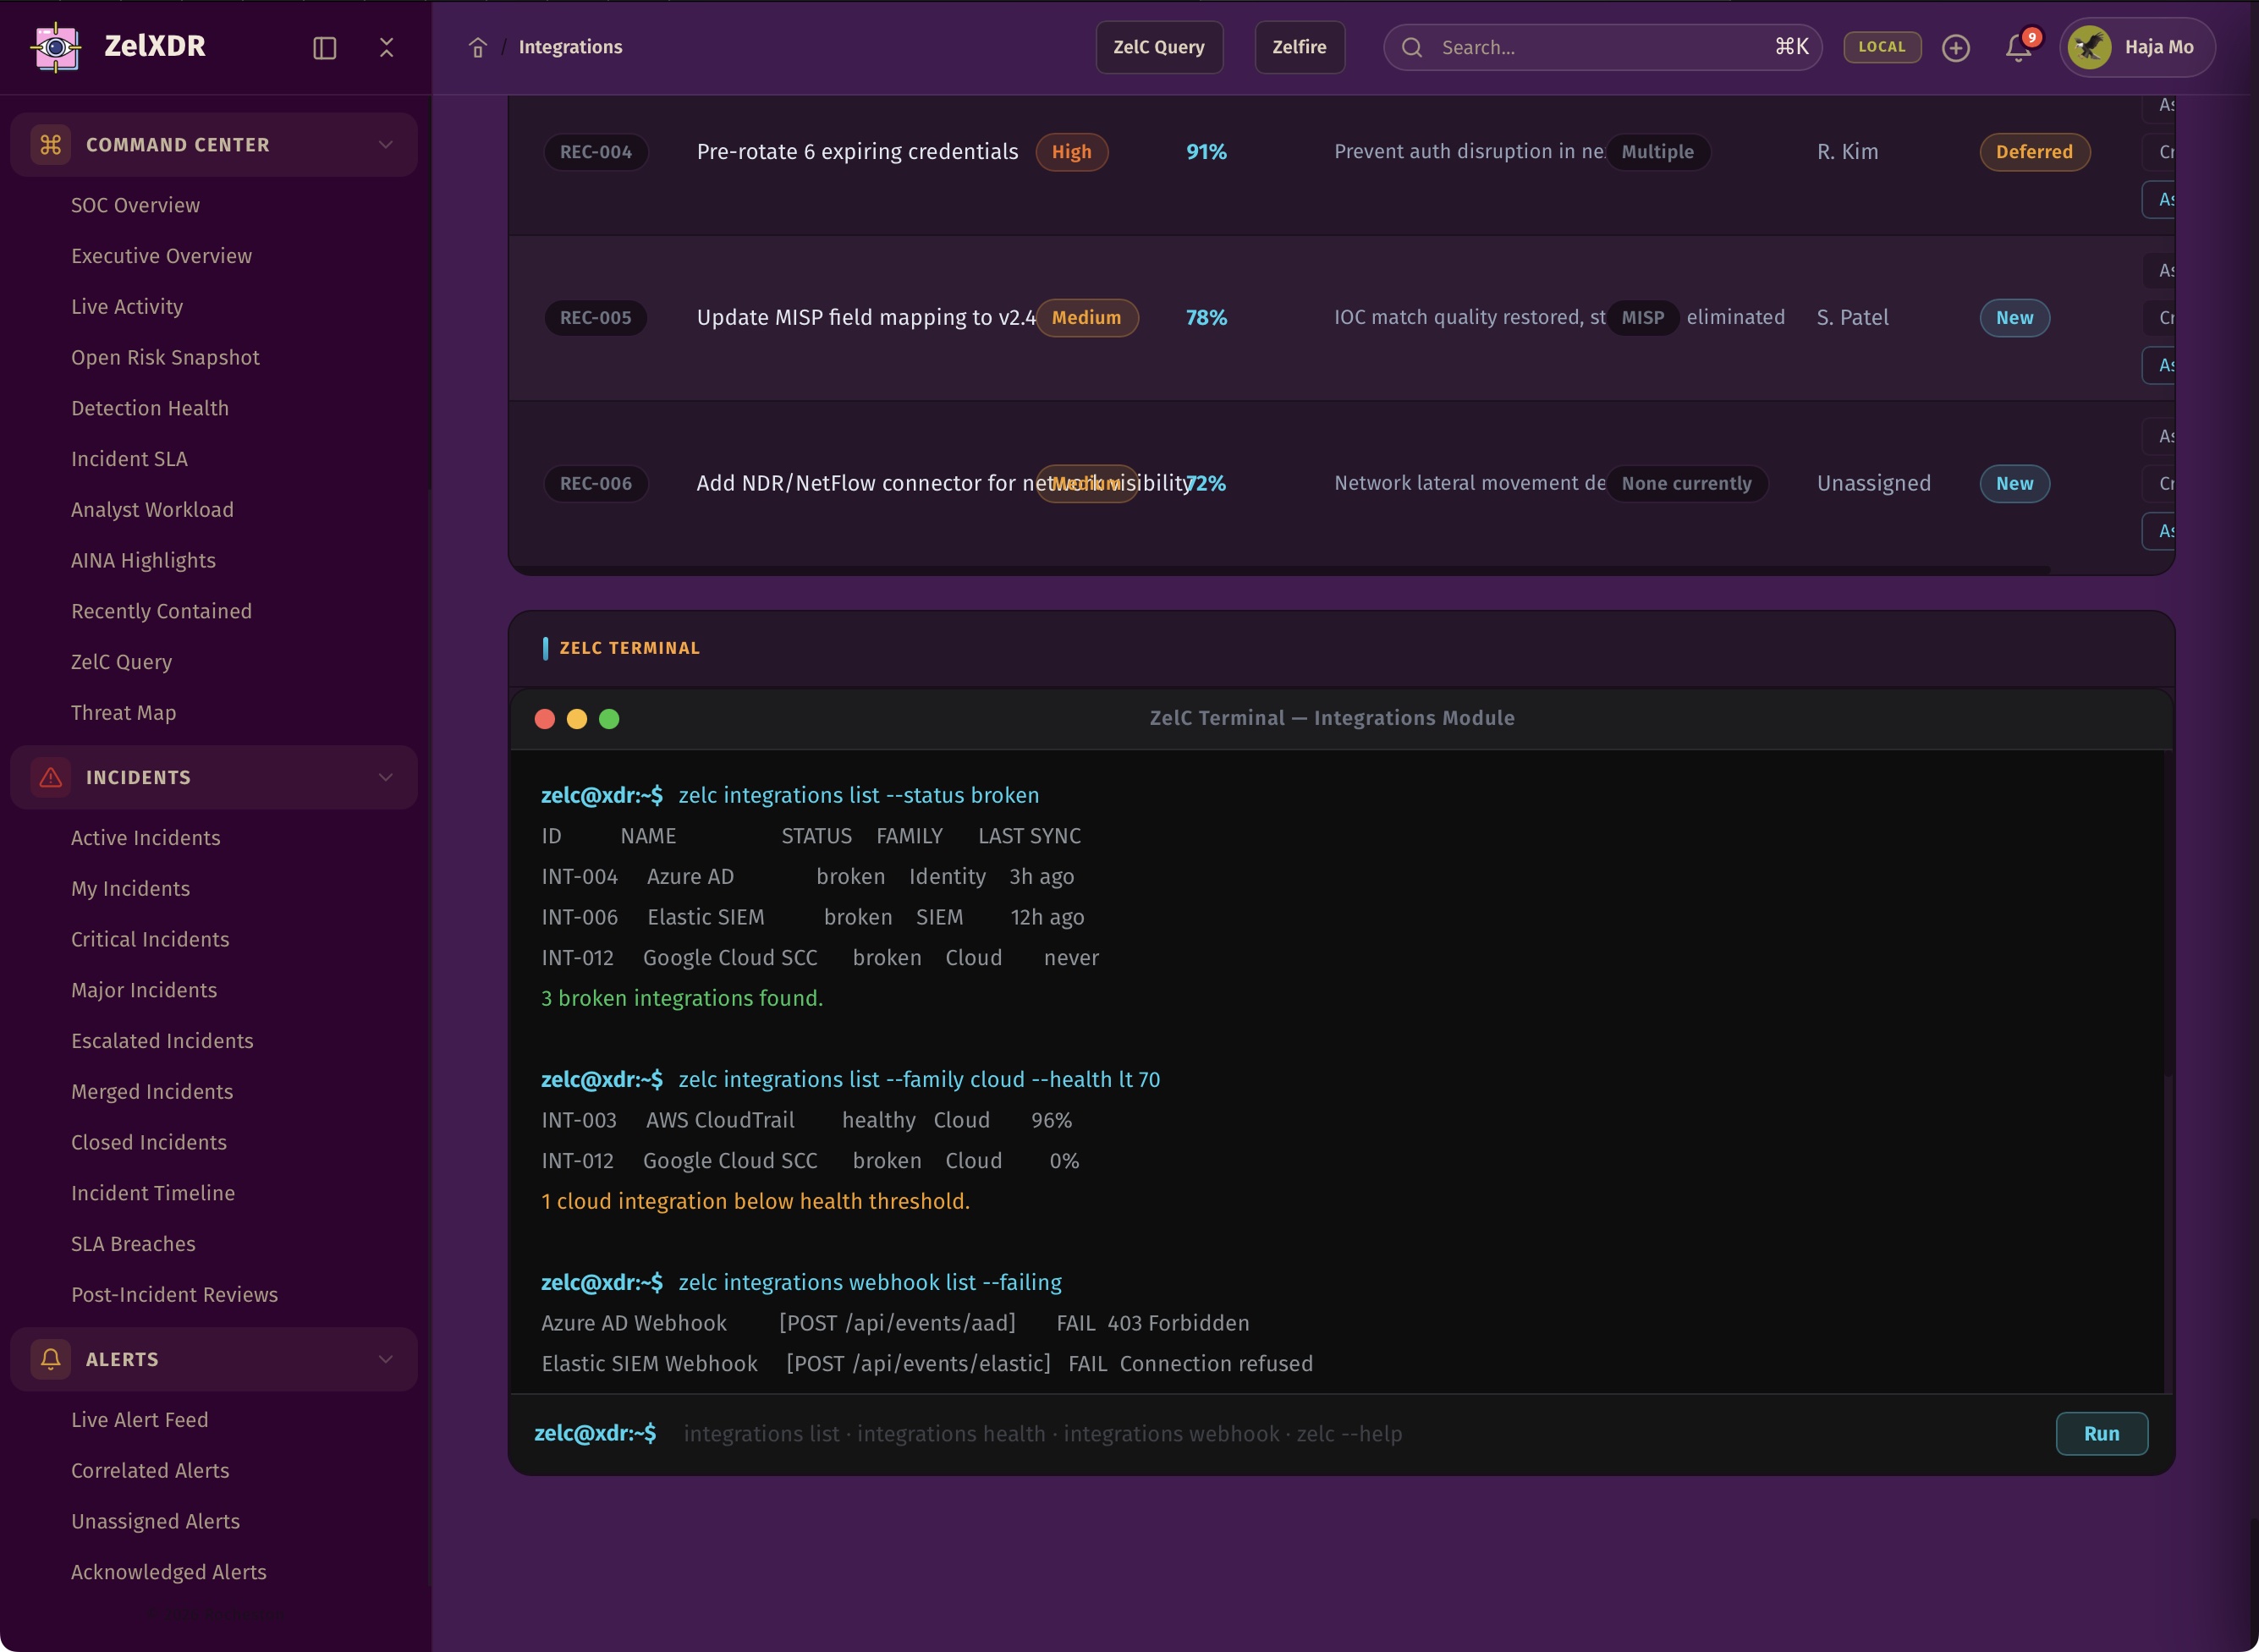
ZelXDR connects with cloud platforms, SIEMs, EDRs, ticketing systems, identity providers, threat intelligence feeds, APIs, webhooks, and internal systems to unify security operations.
Security gets stronger when the systems stop working alone.
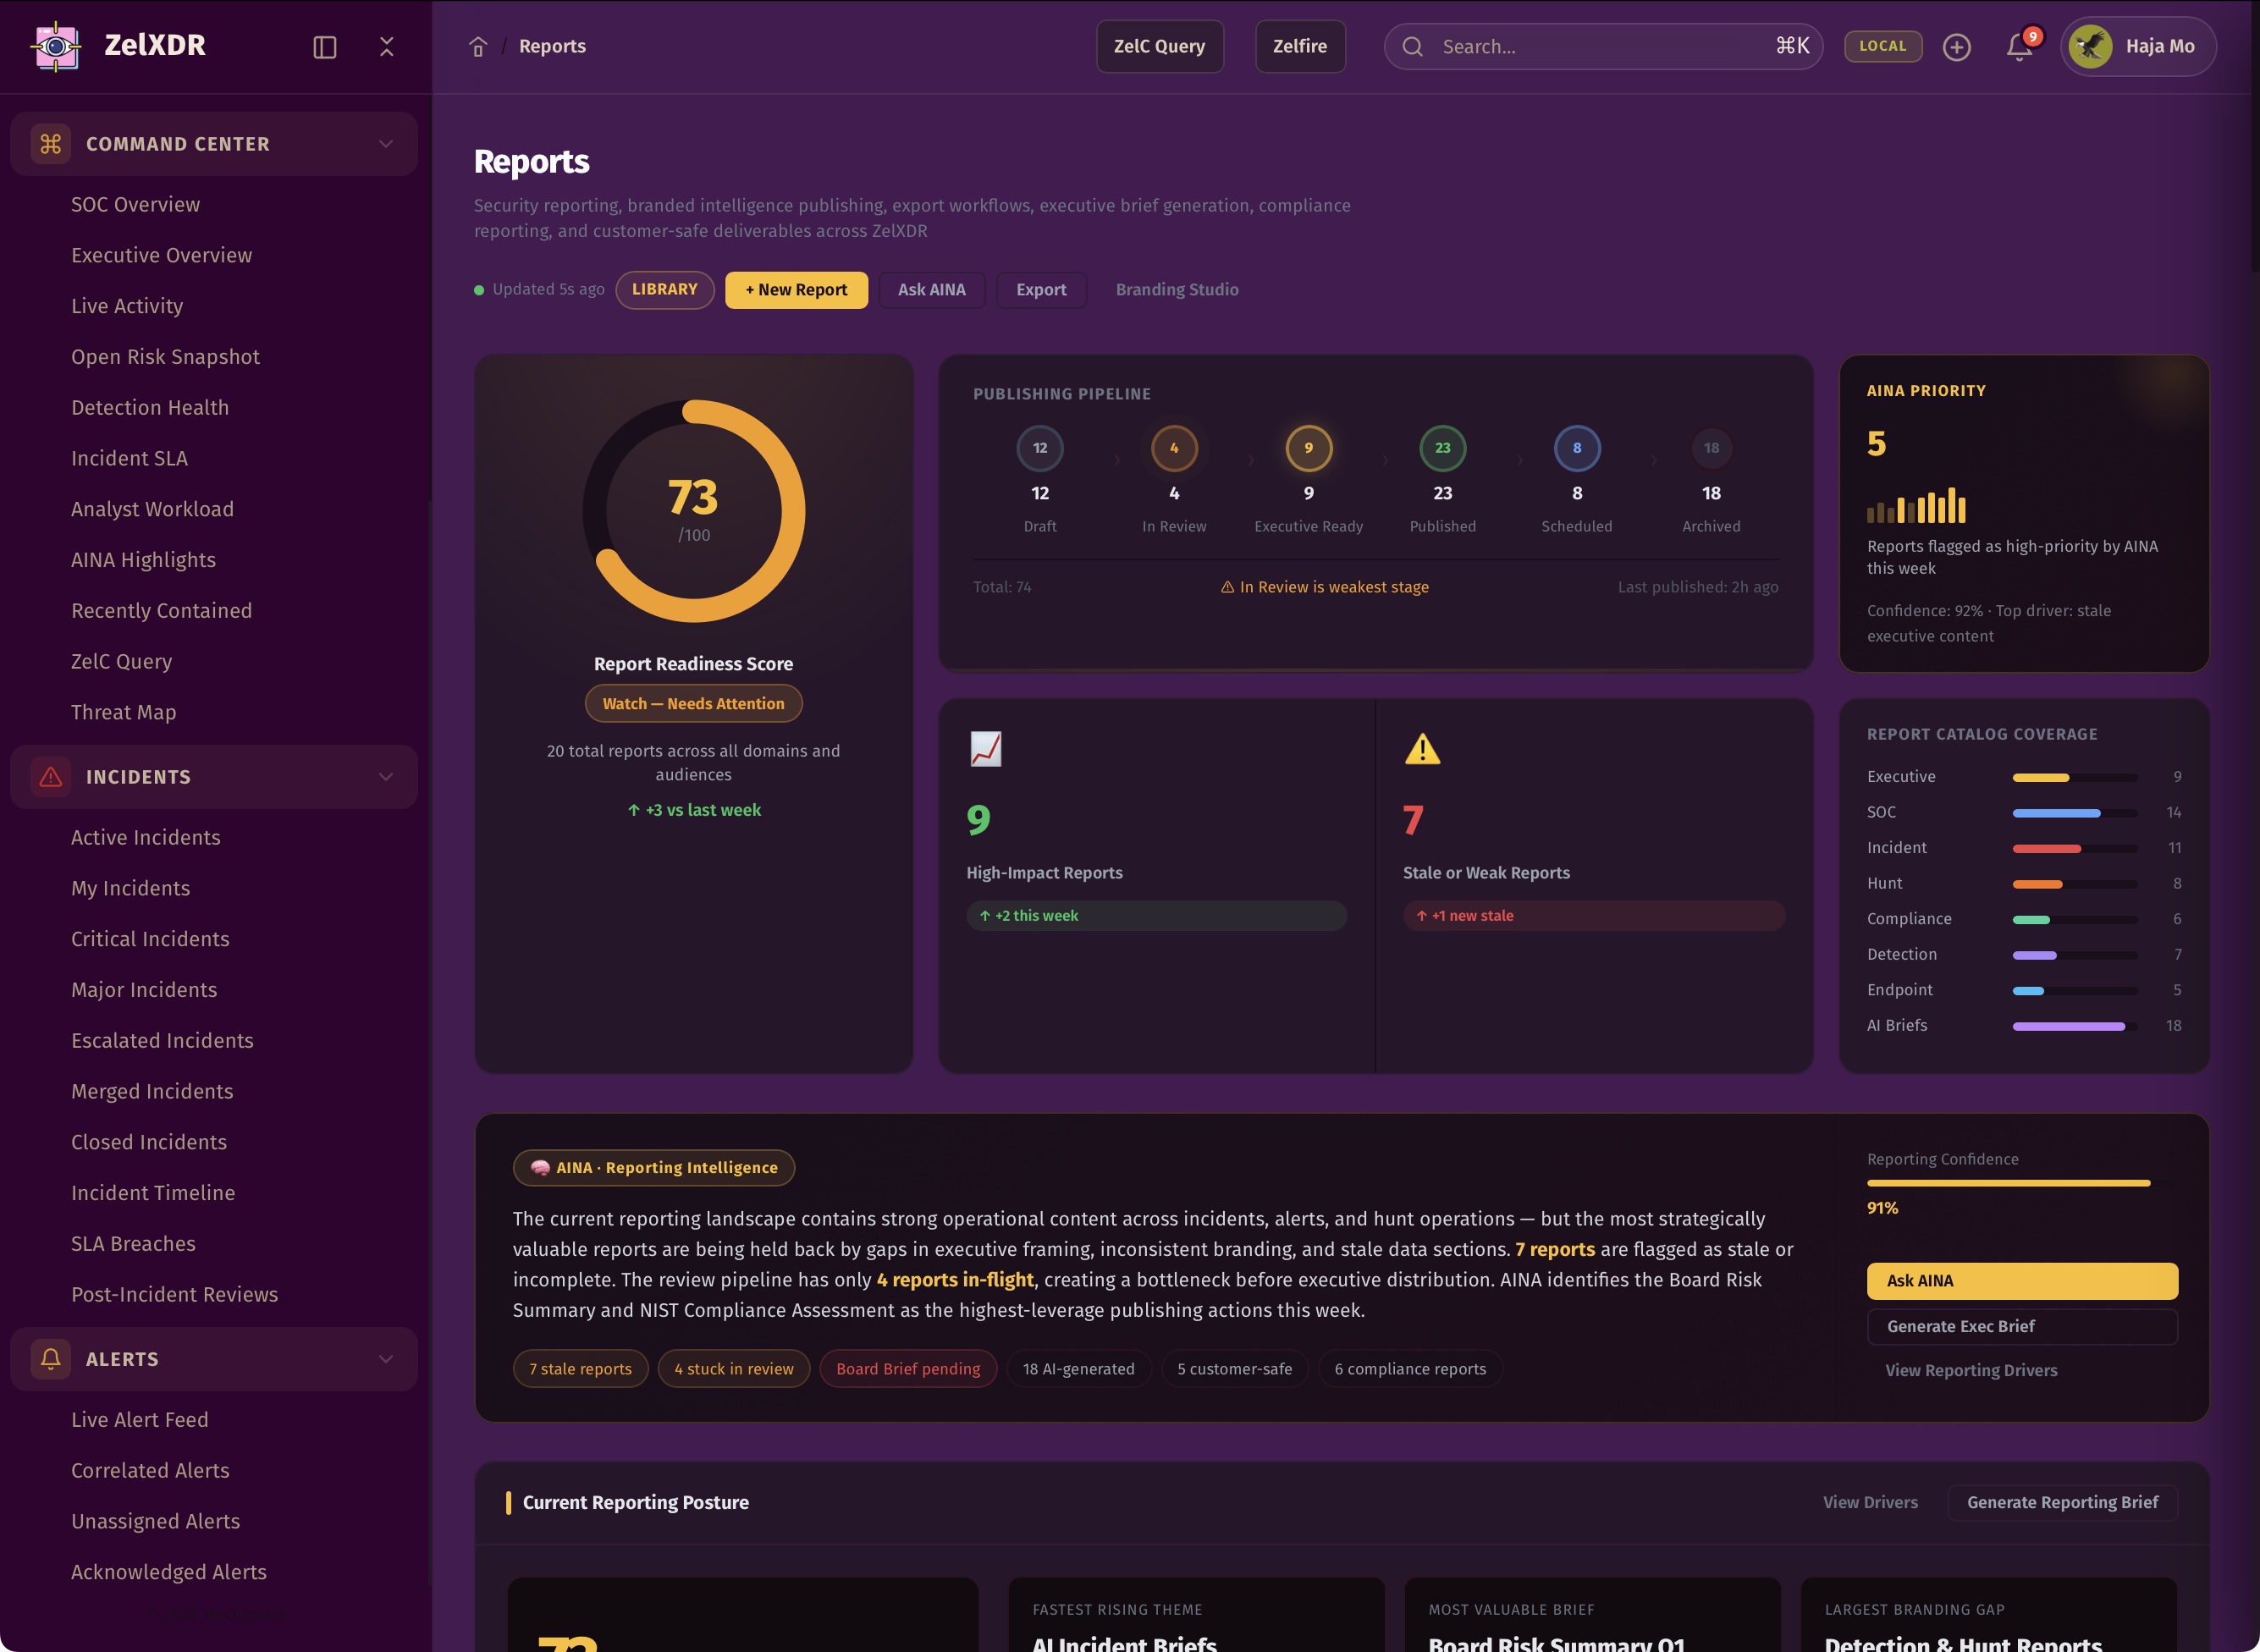
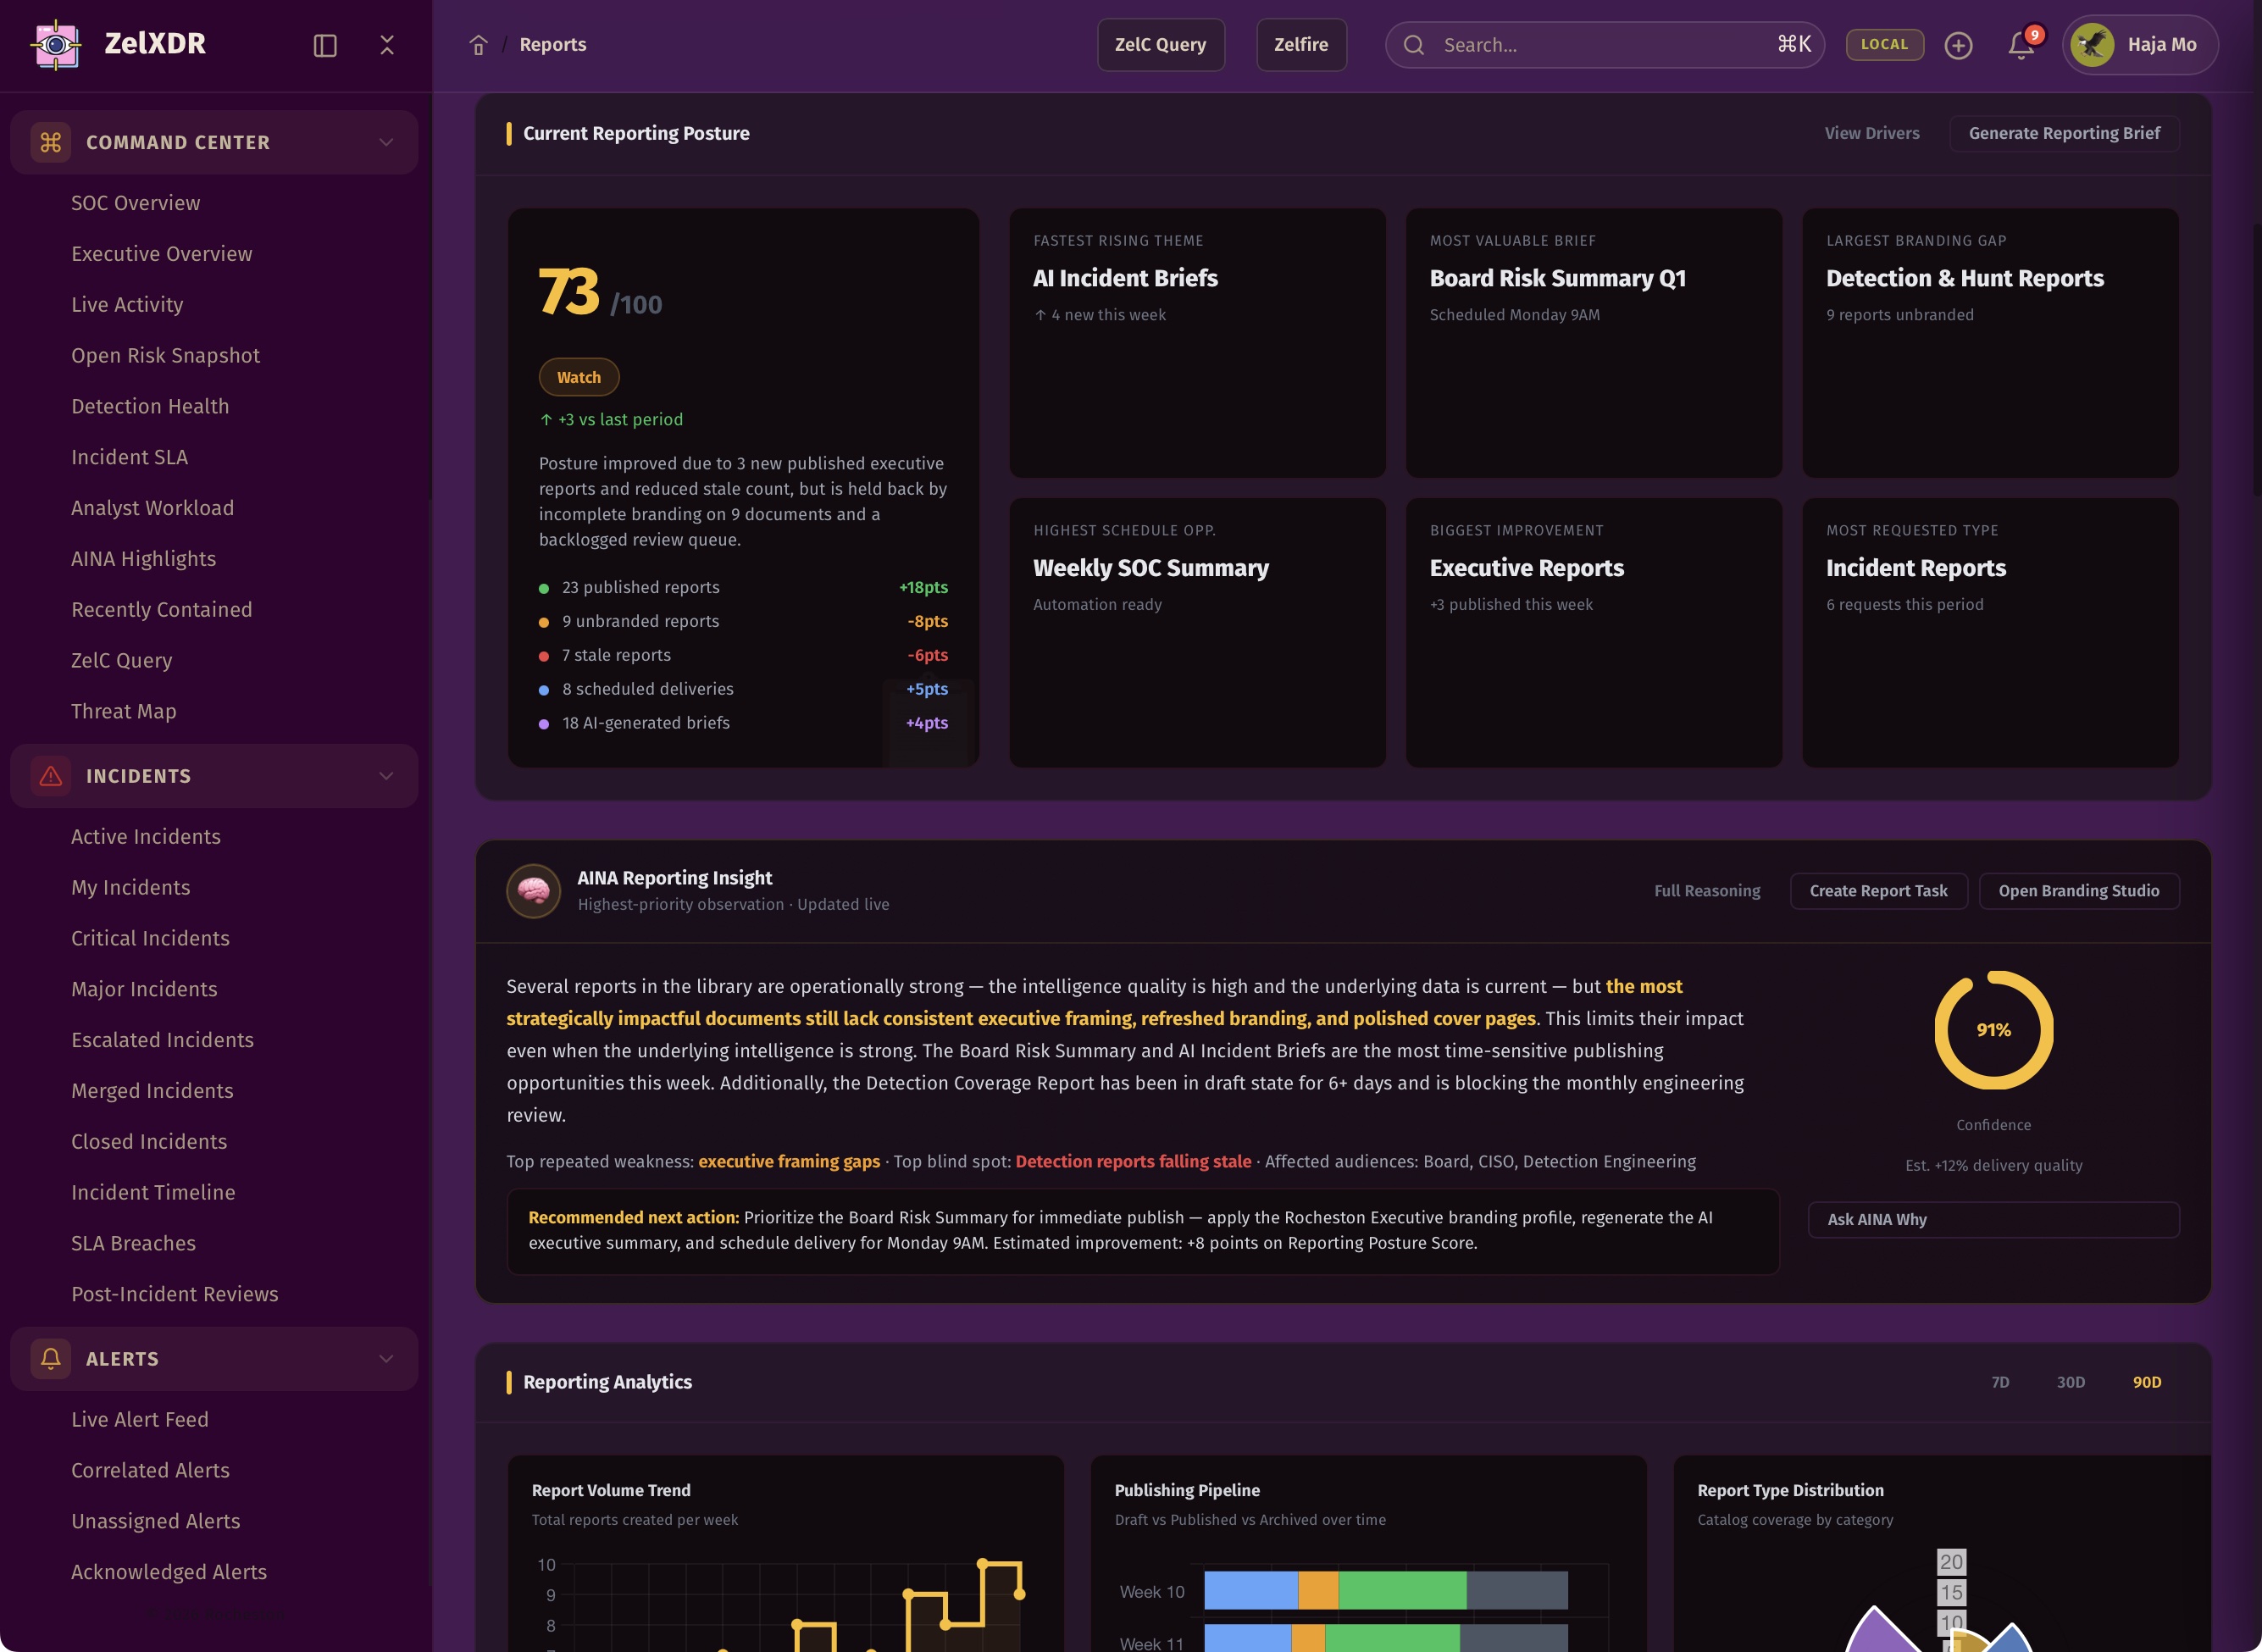
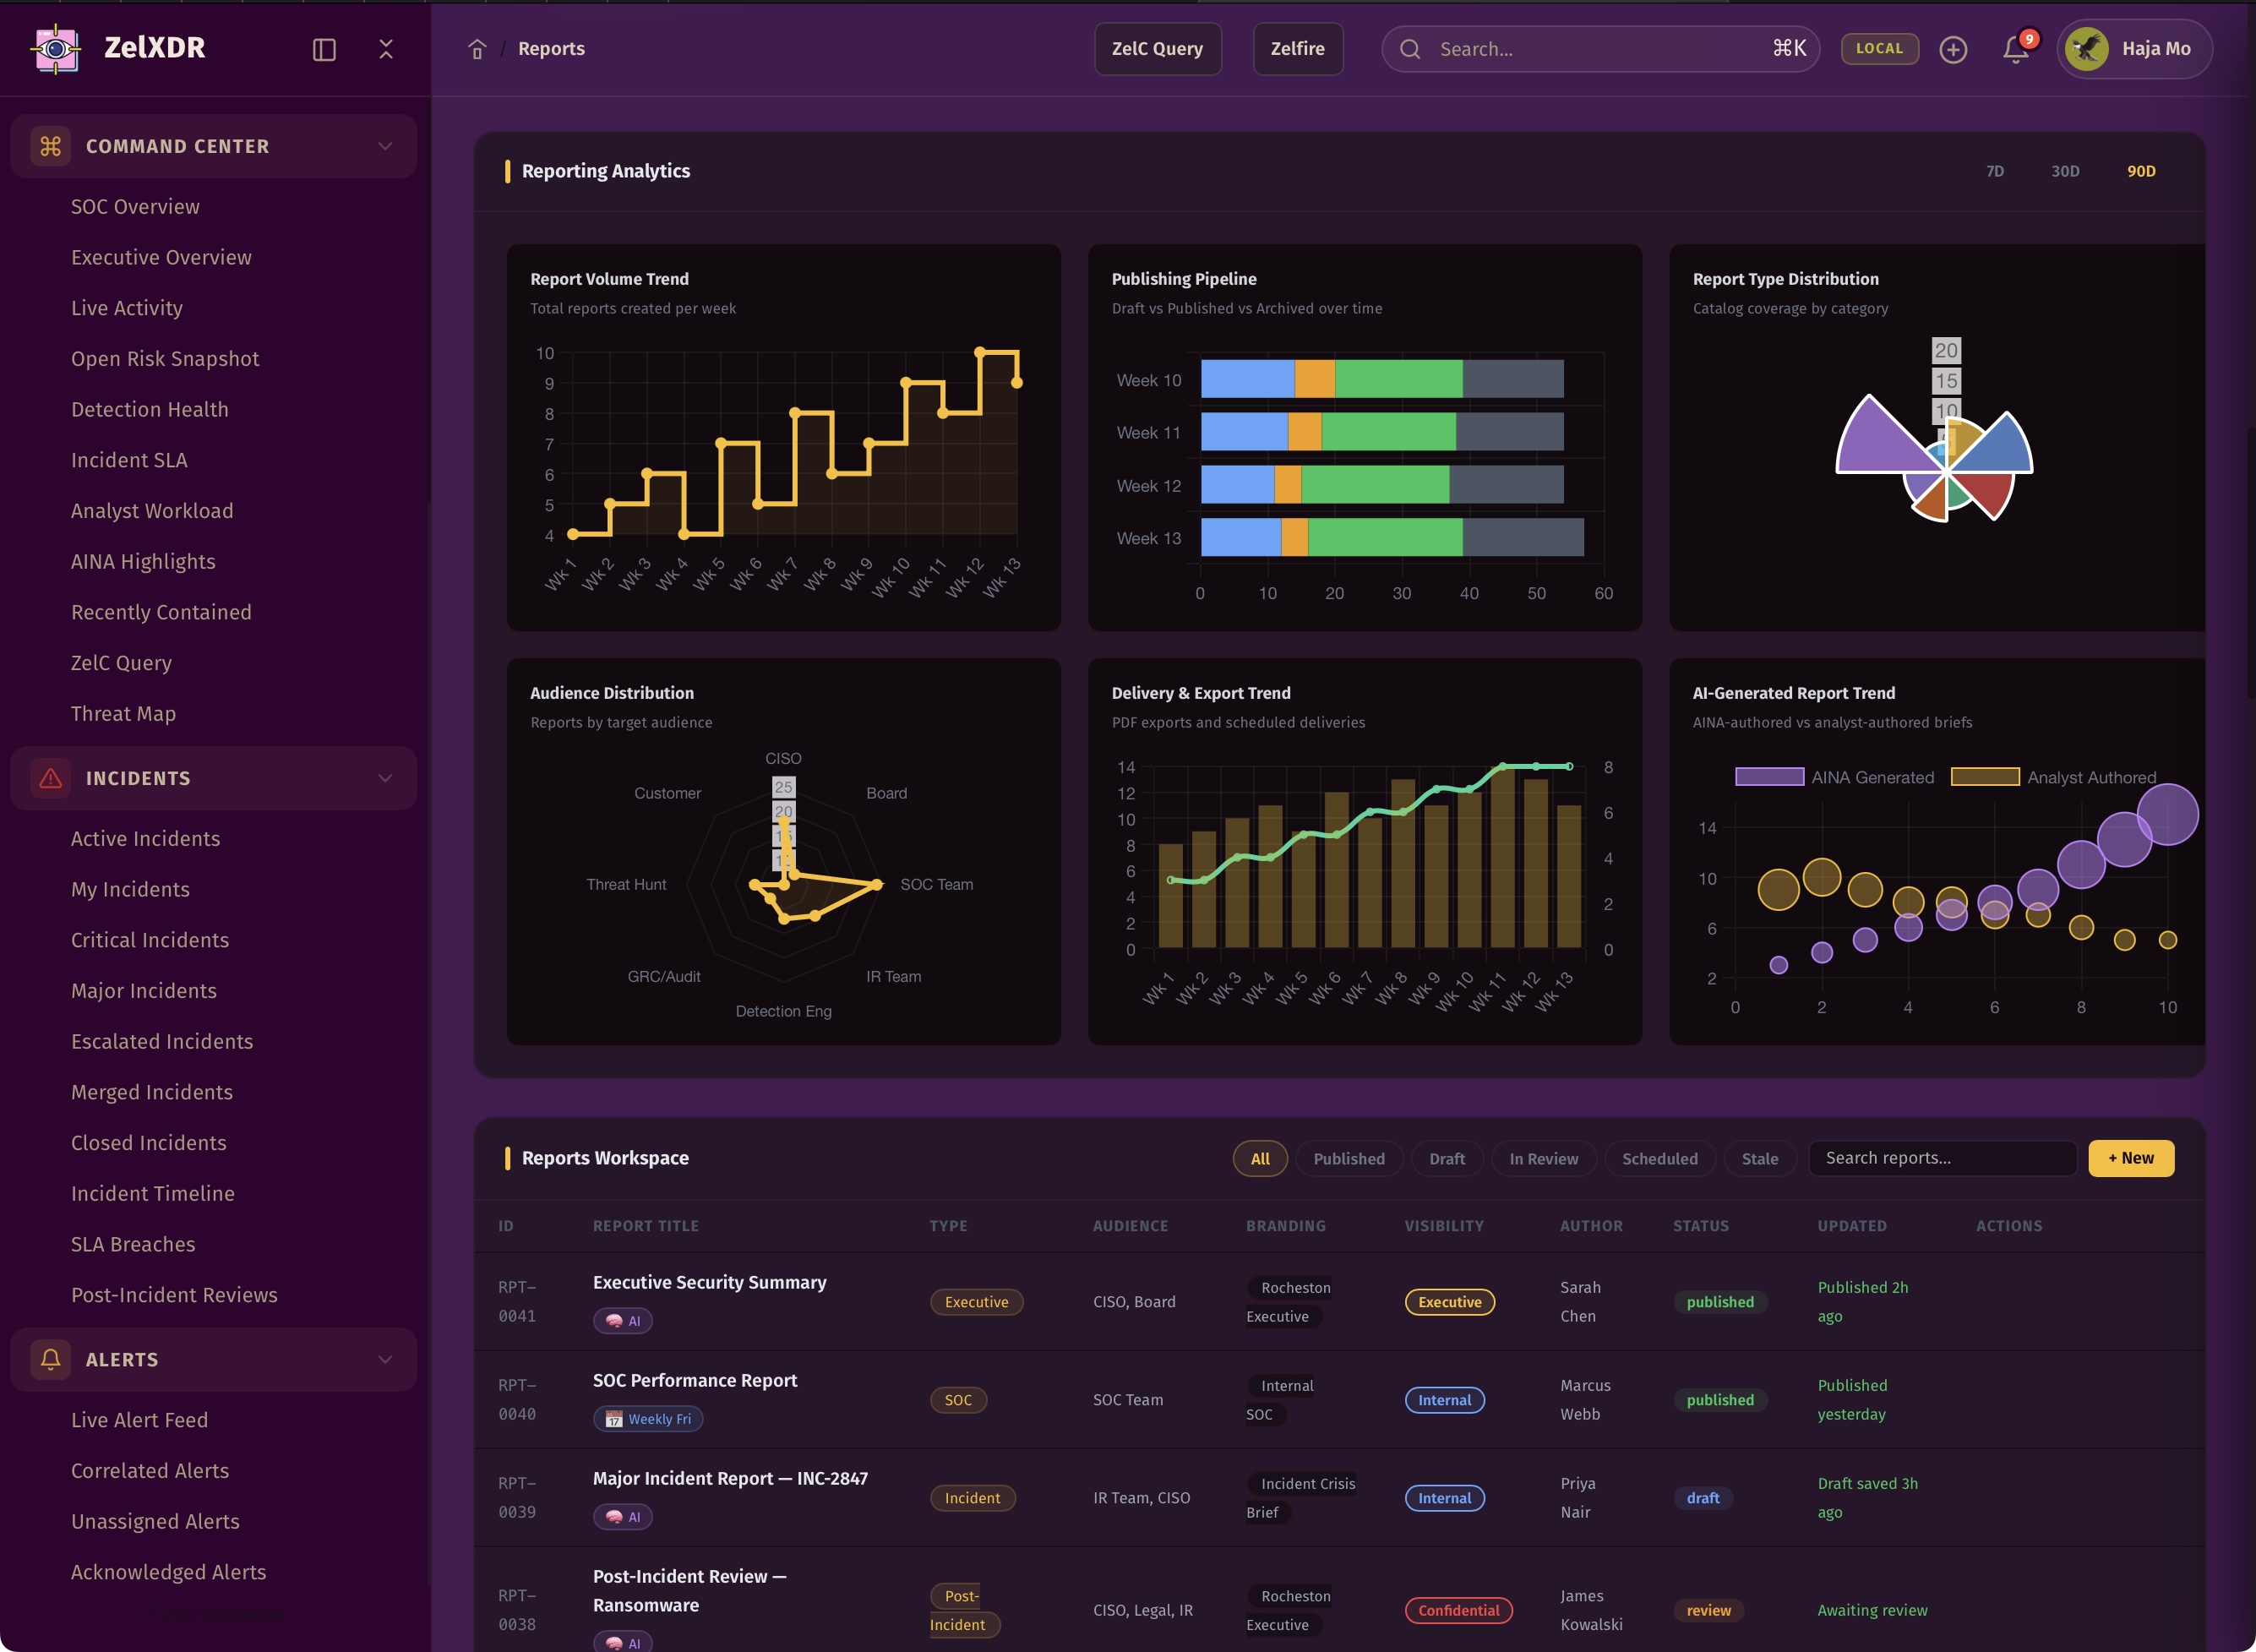
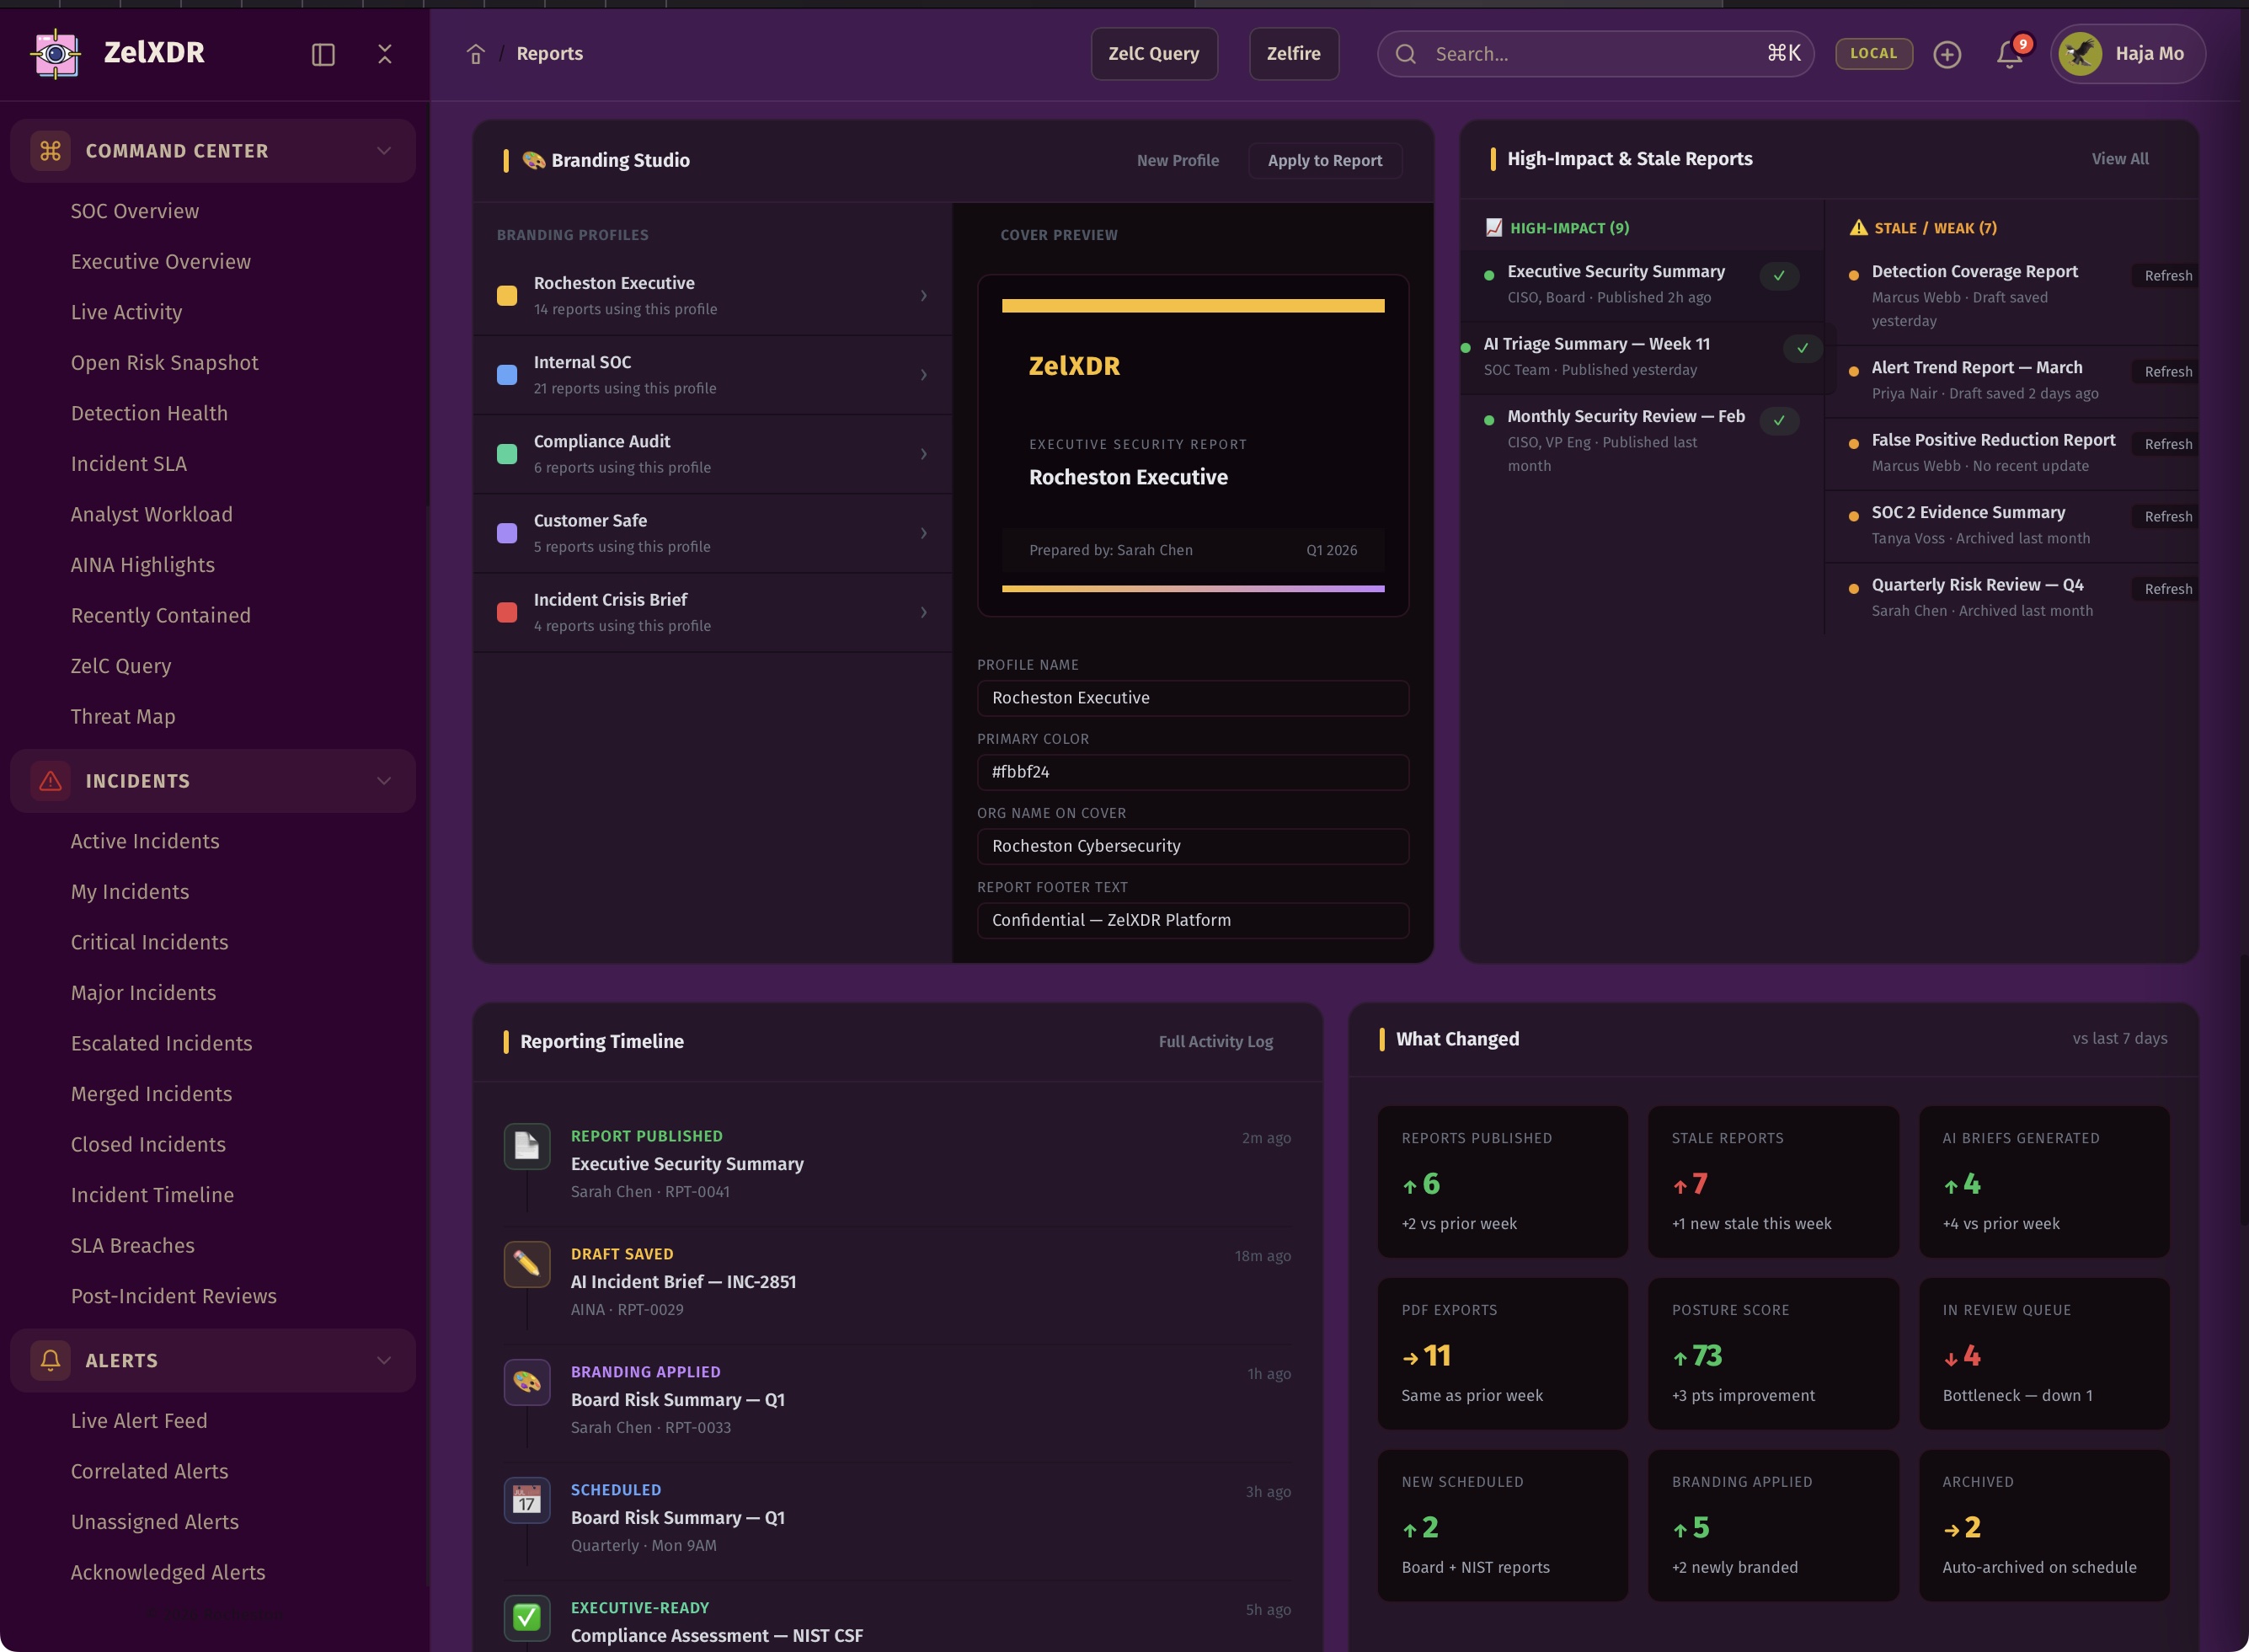
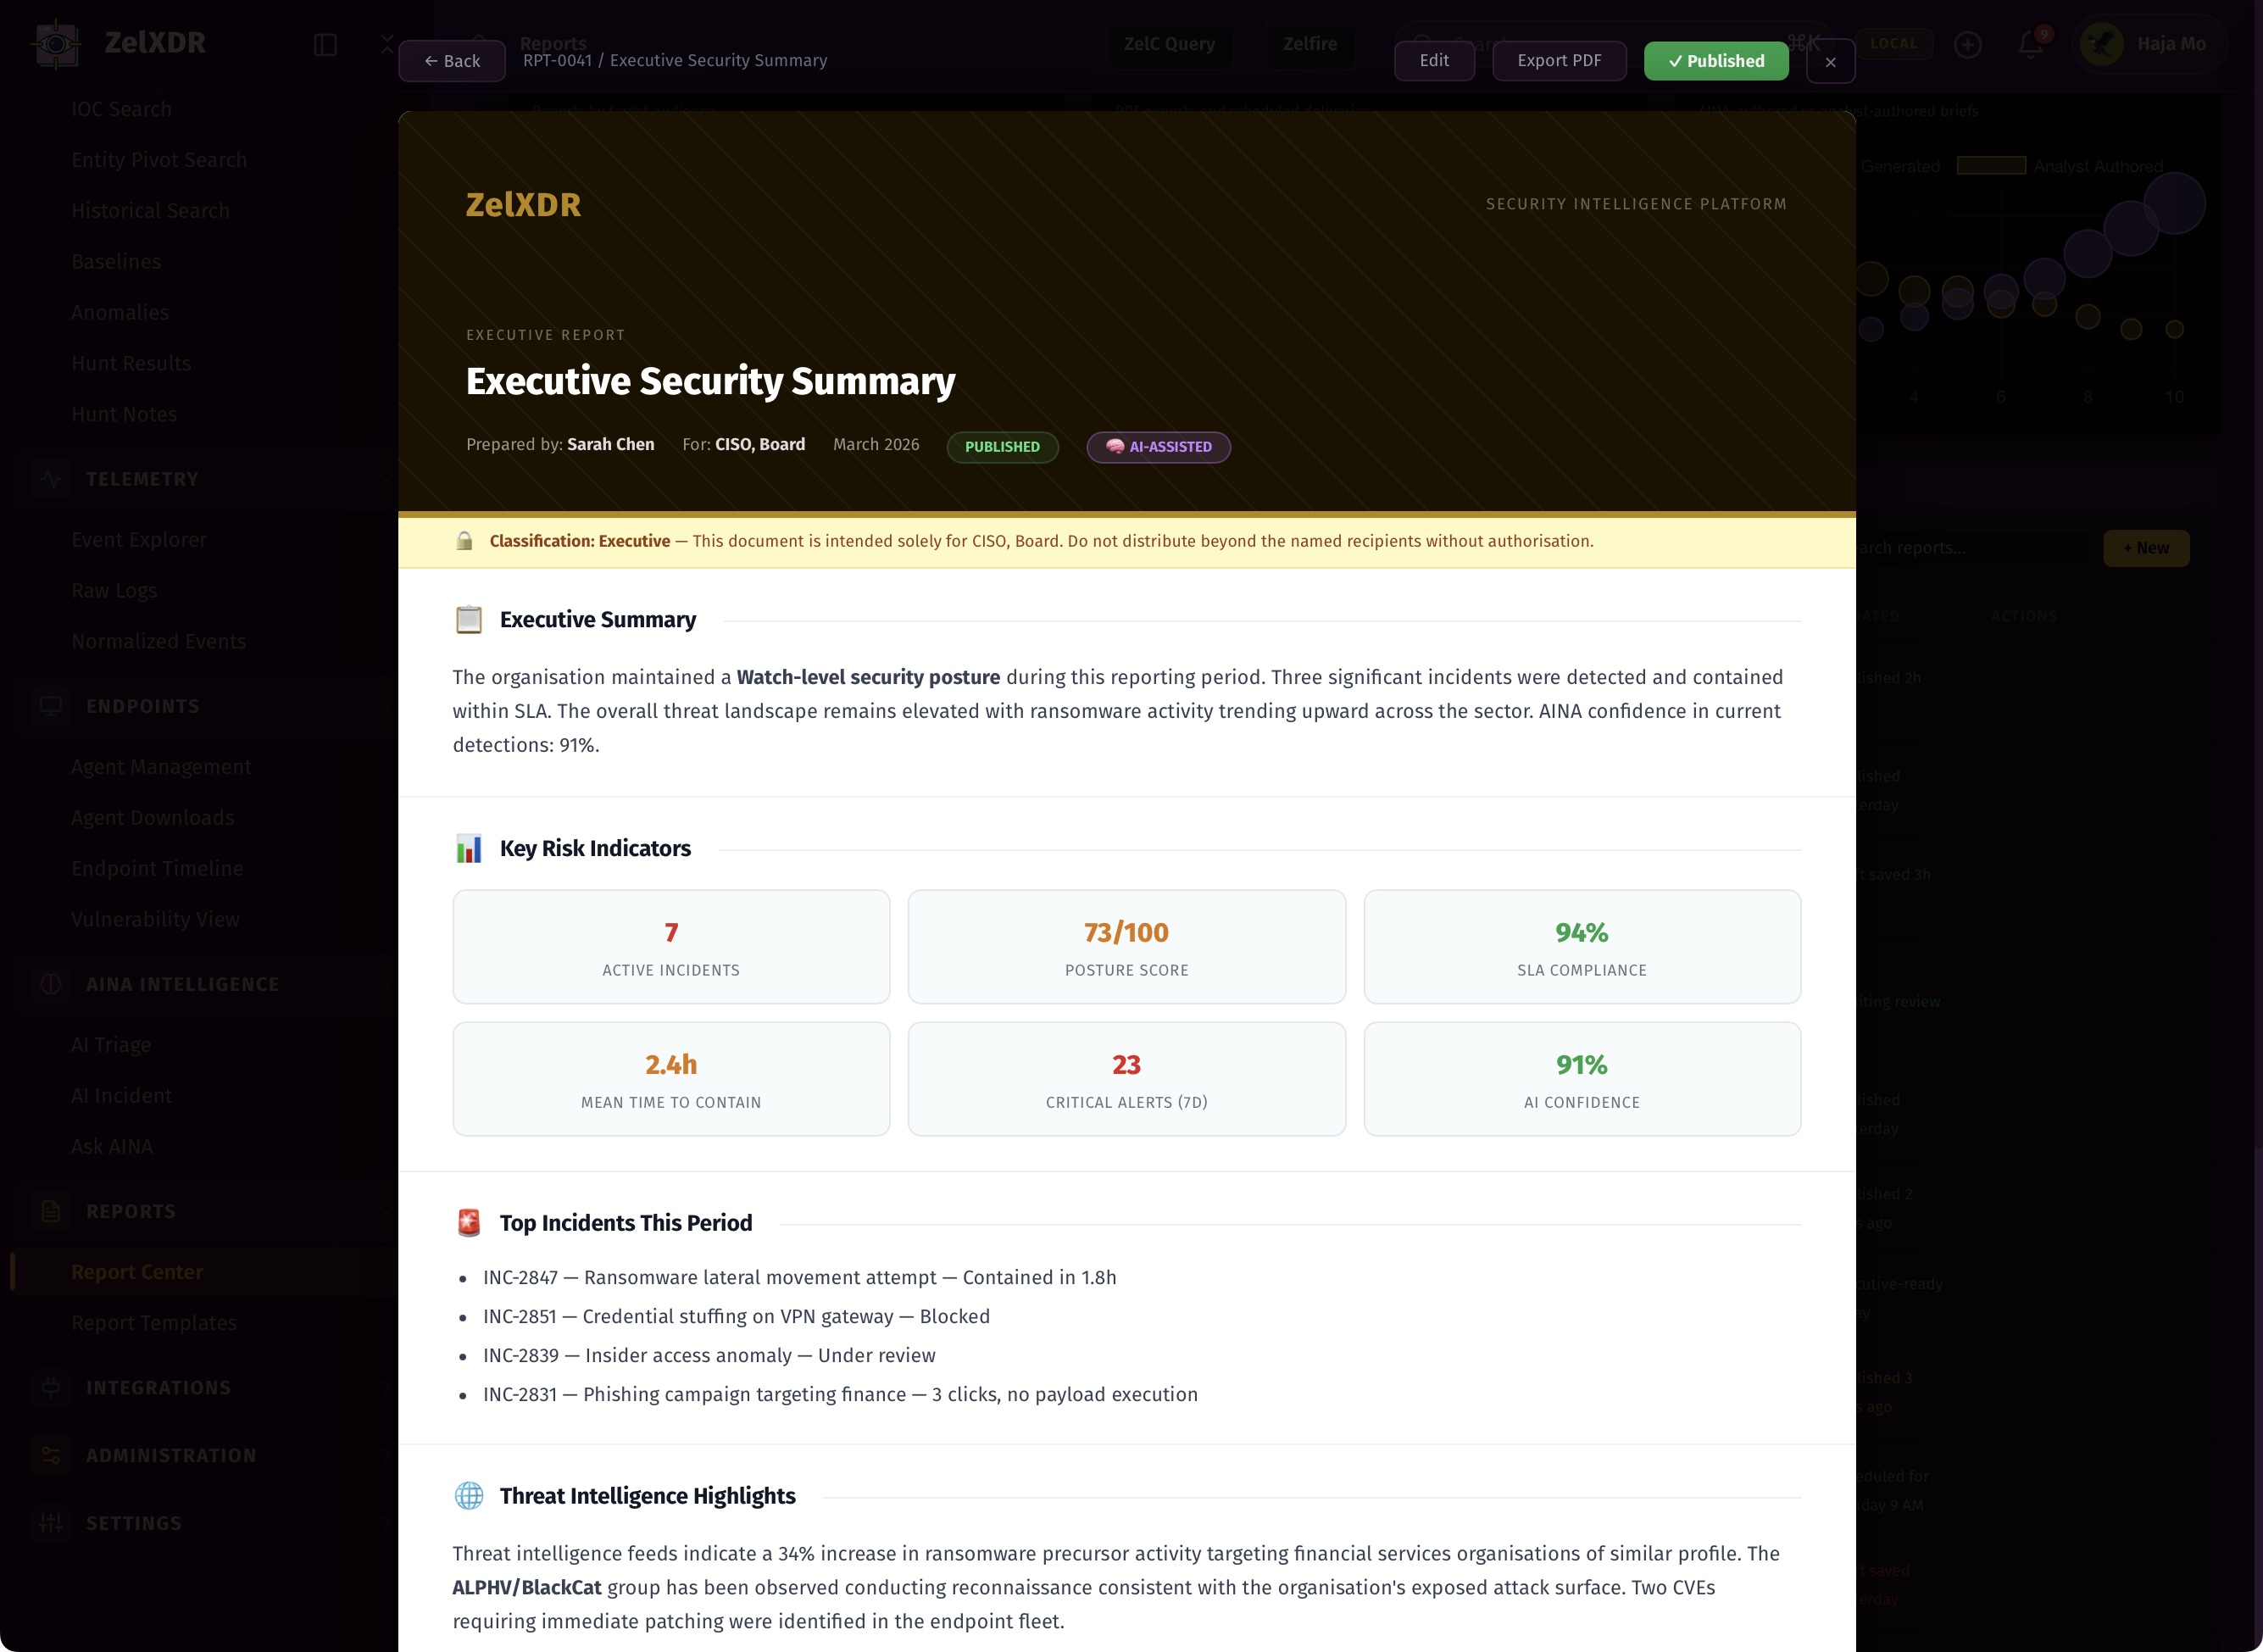
ZelXDR supports rich operational reporting, executive summaries, incident briefs, compliance reporting, and customer-safe exports so intelligence can be communicated clearly and professionally.
Security value grows when it can be explained.
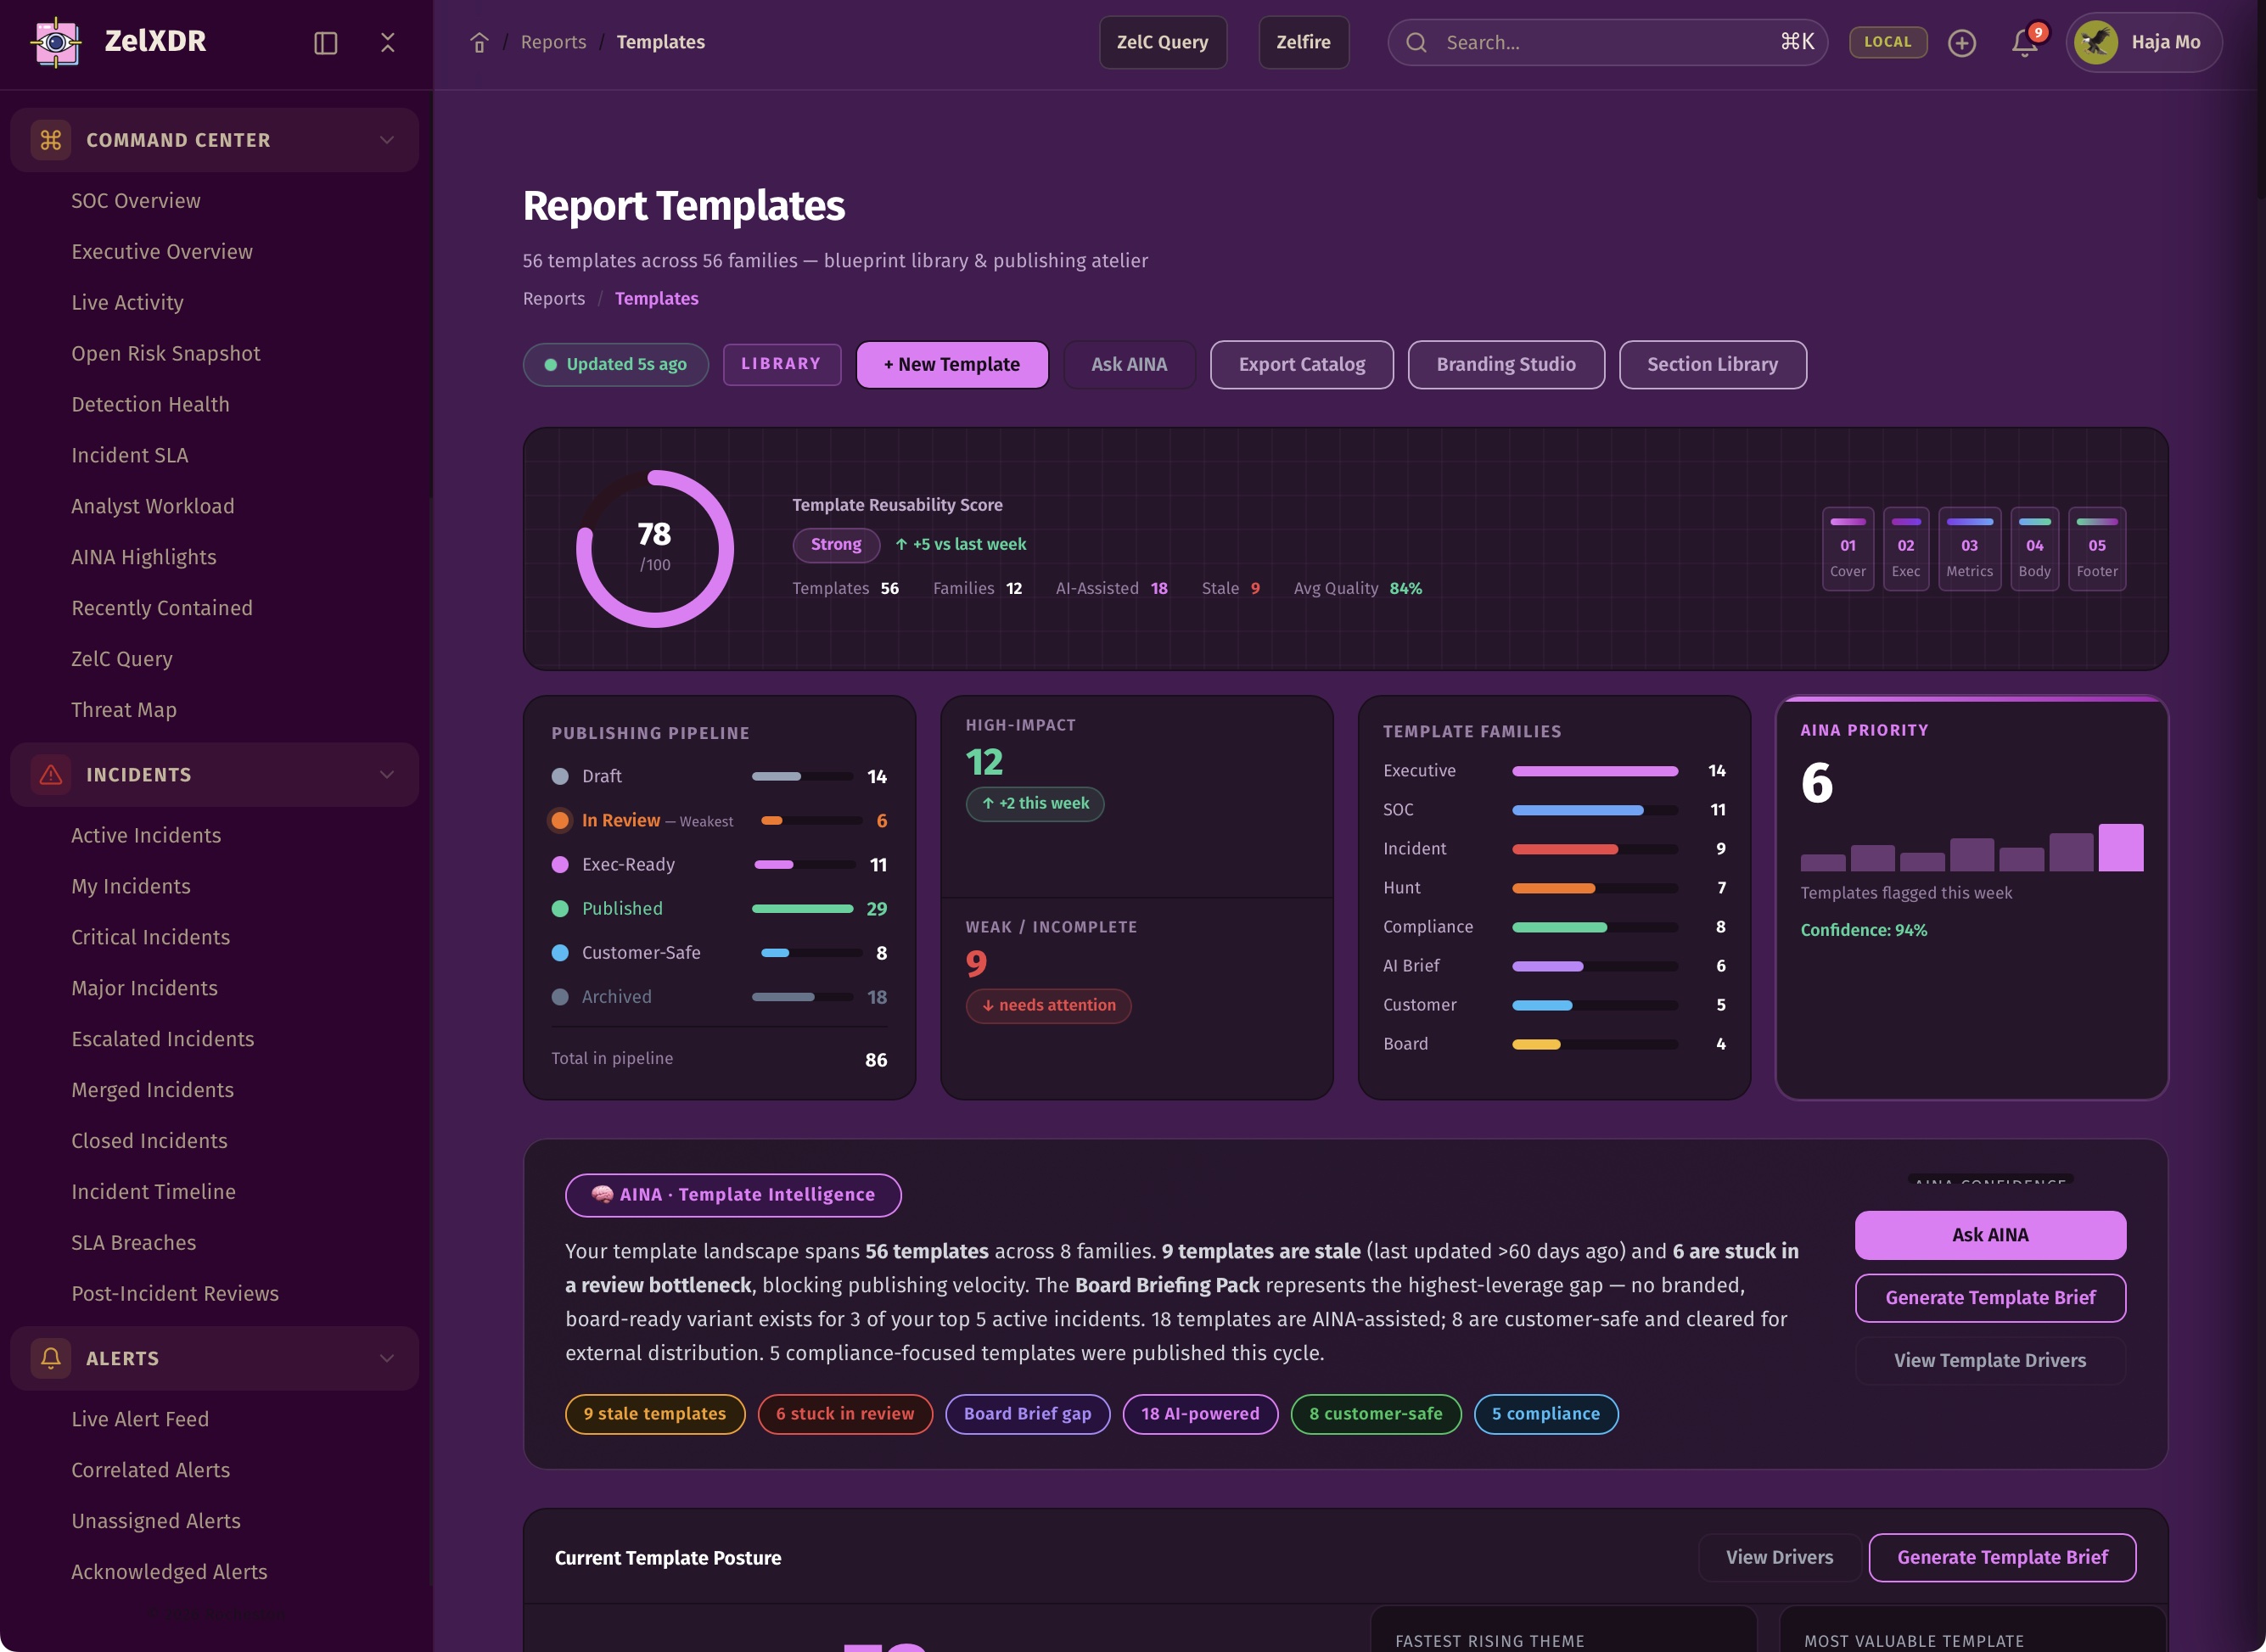
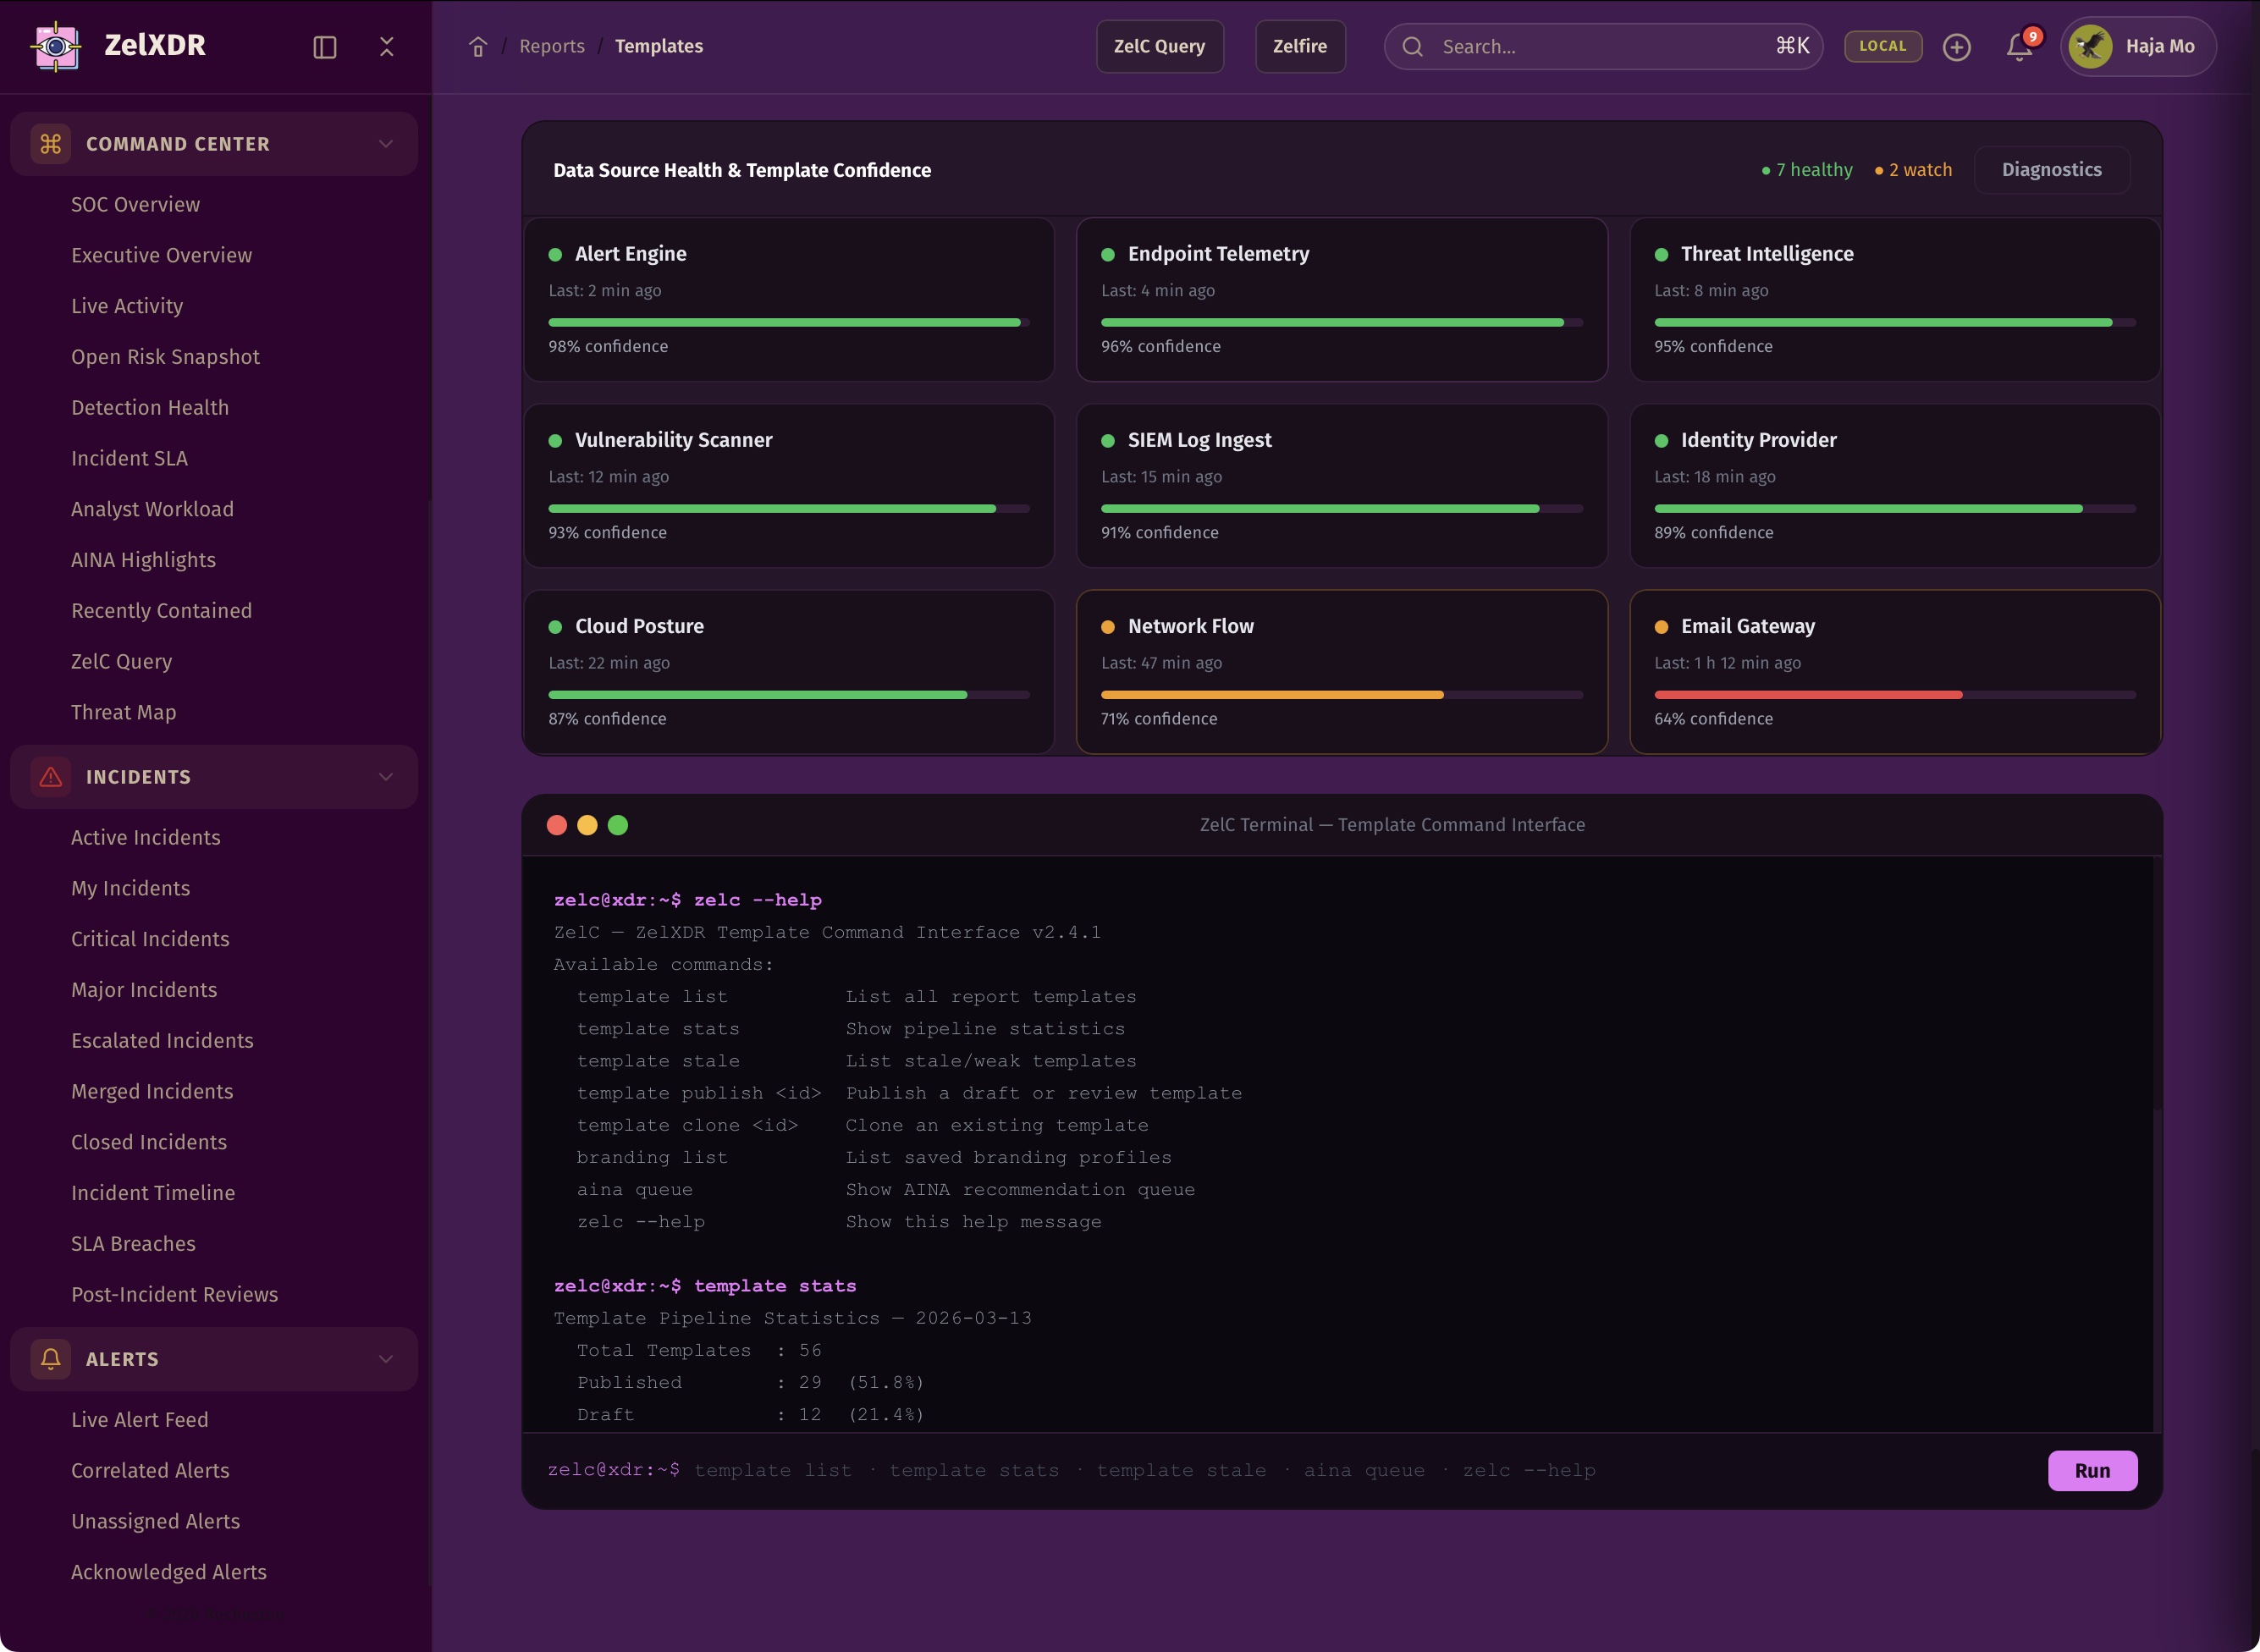
Reusable templates, branding profiles, cover layouts, executive formatting, and audience-aware report design help teams produce polished outputs faster and with more consistency.
Great reporting is both intelligence and presentation.
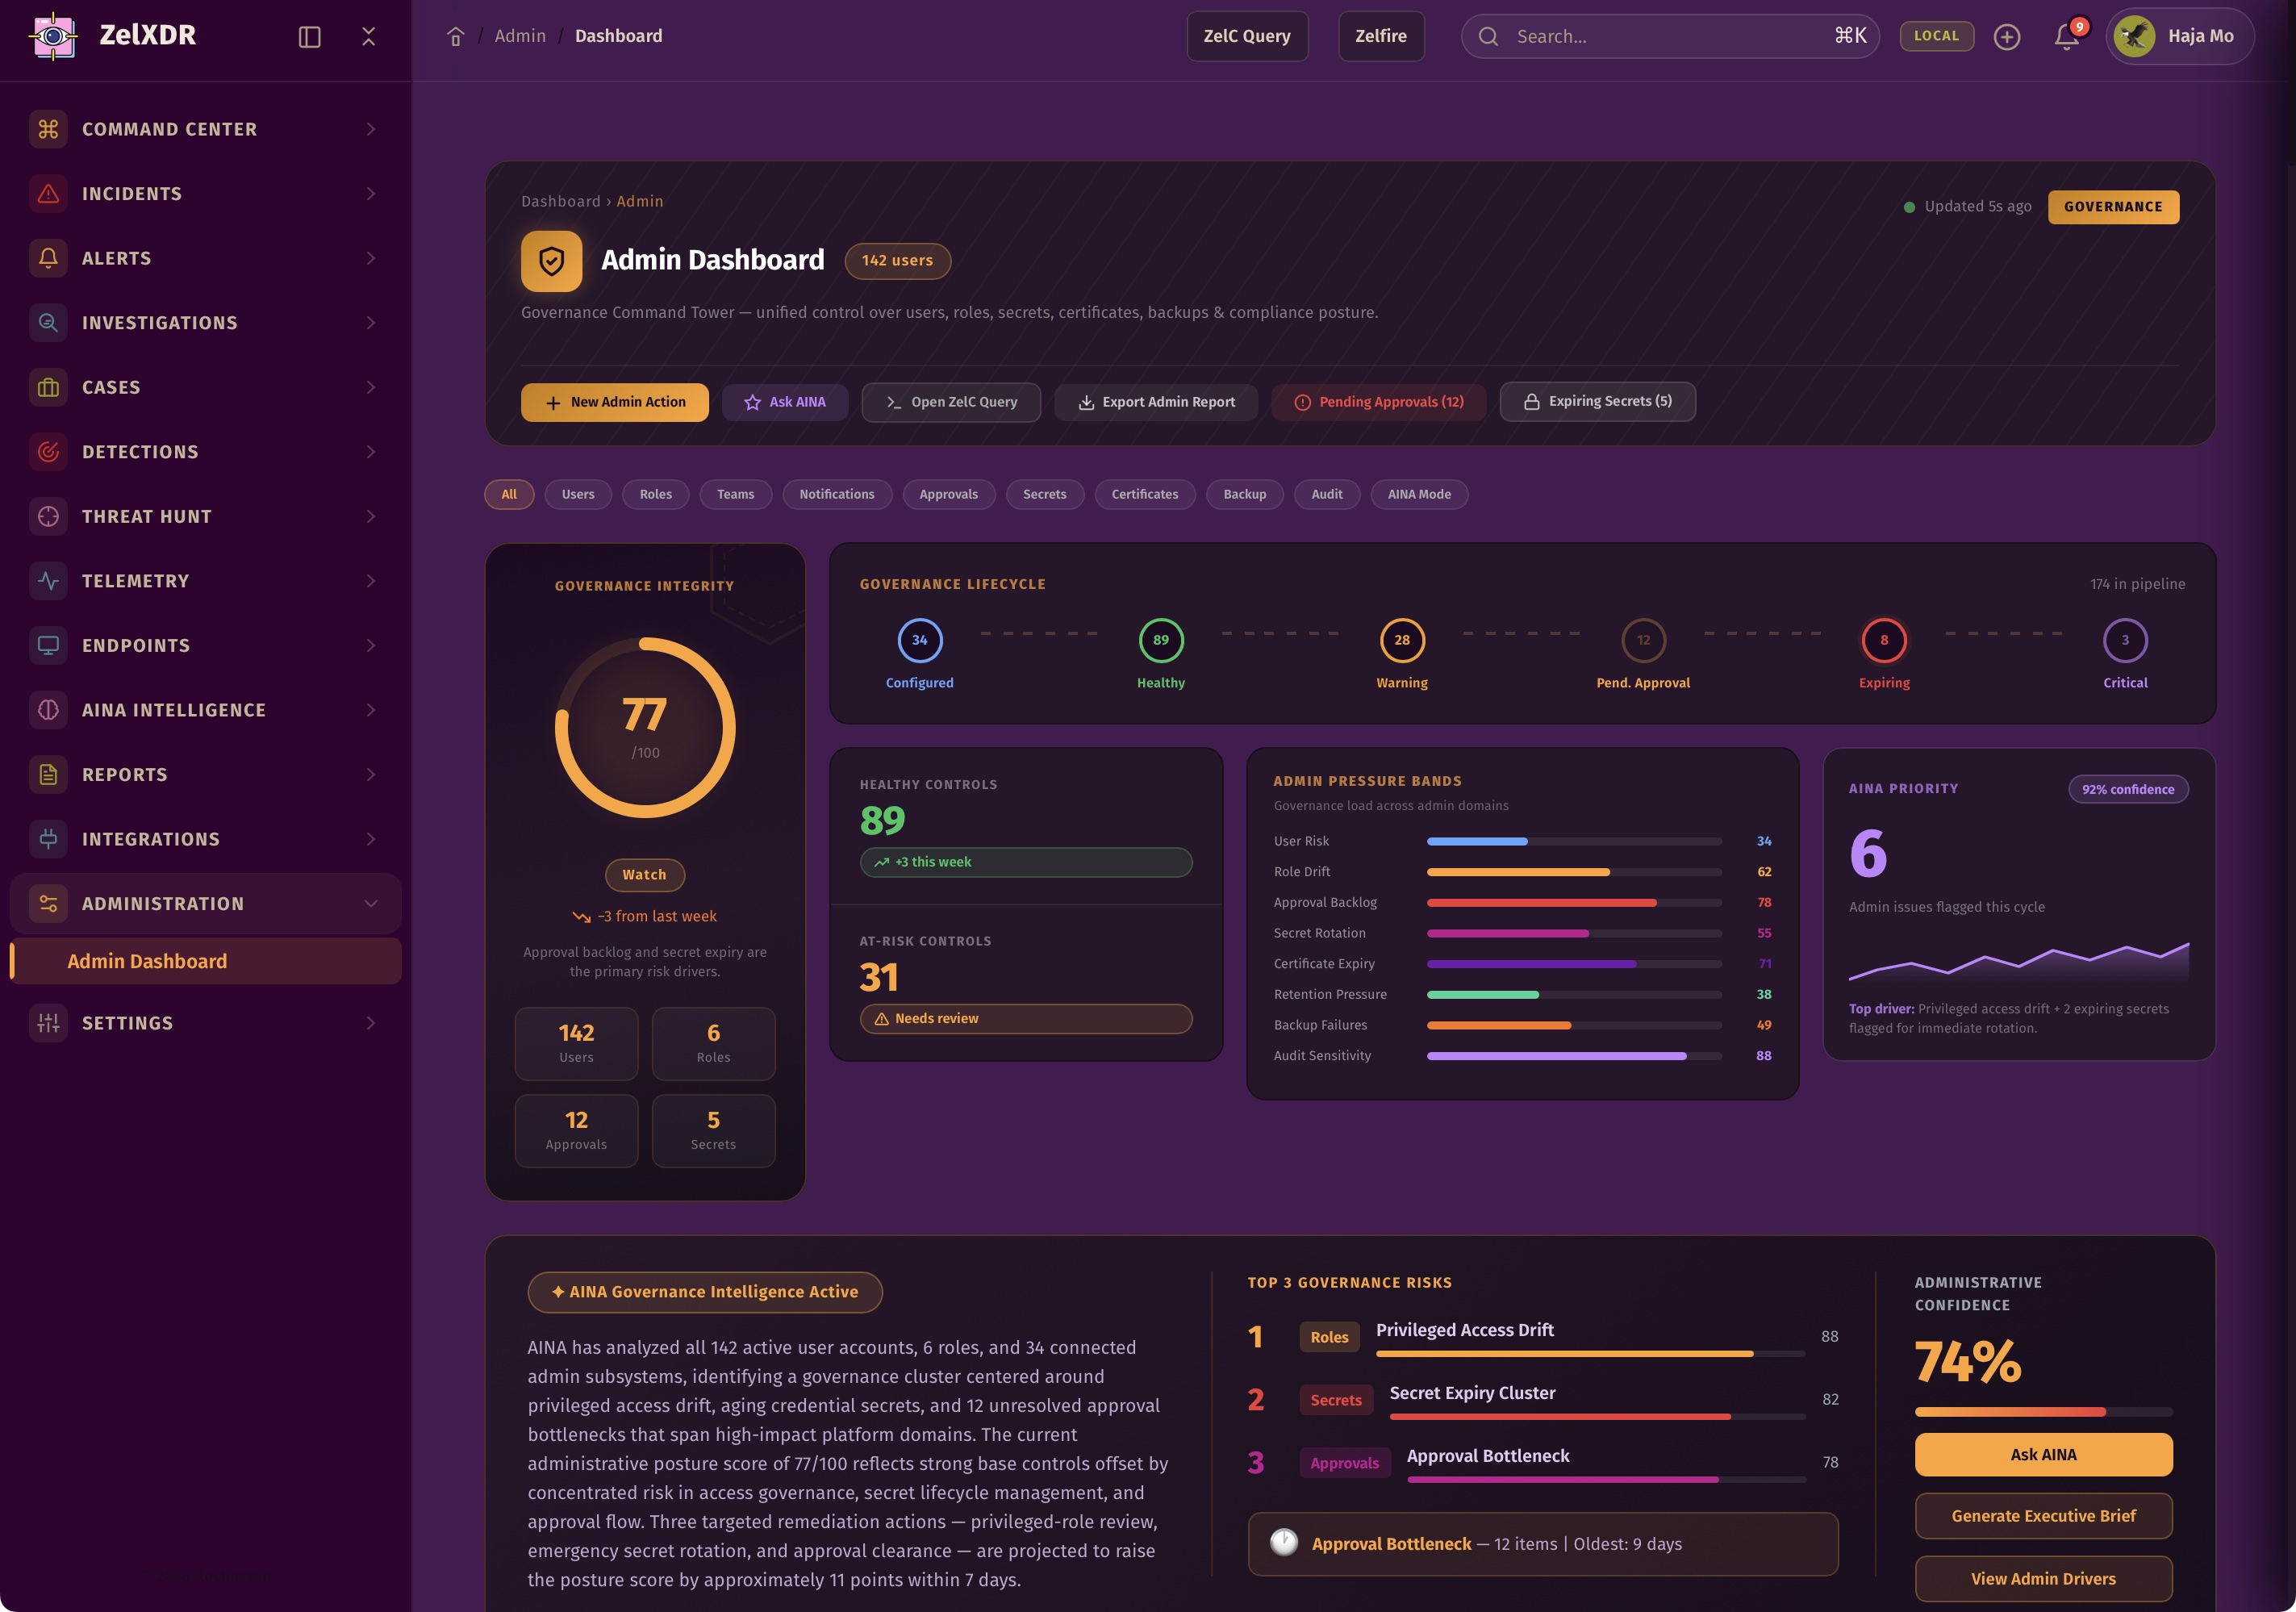
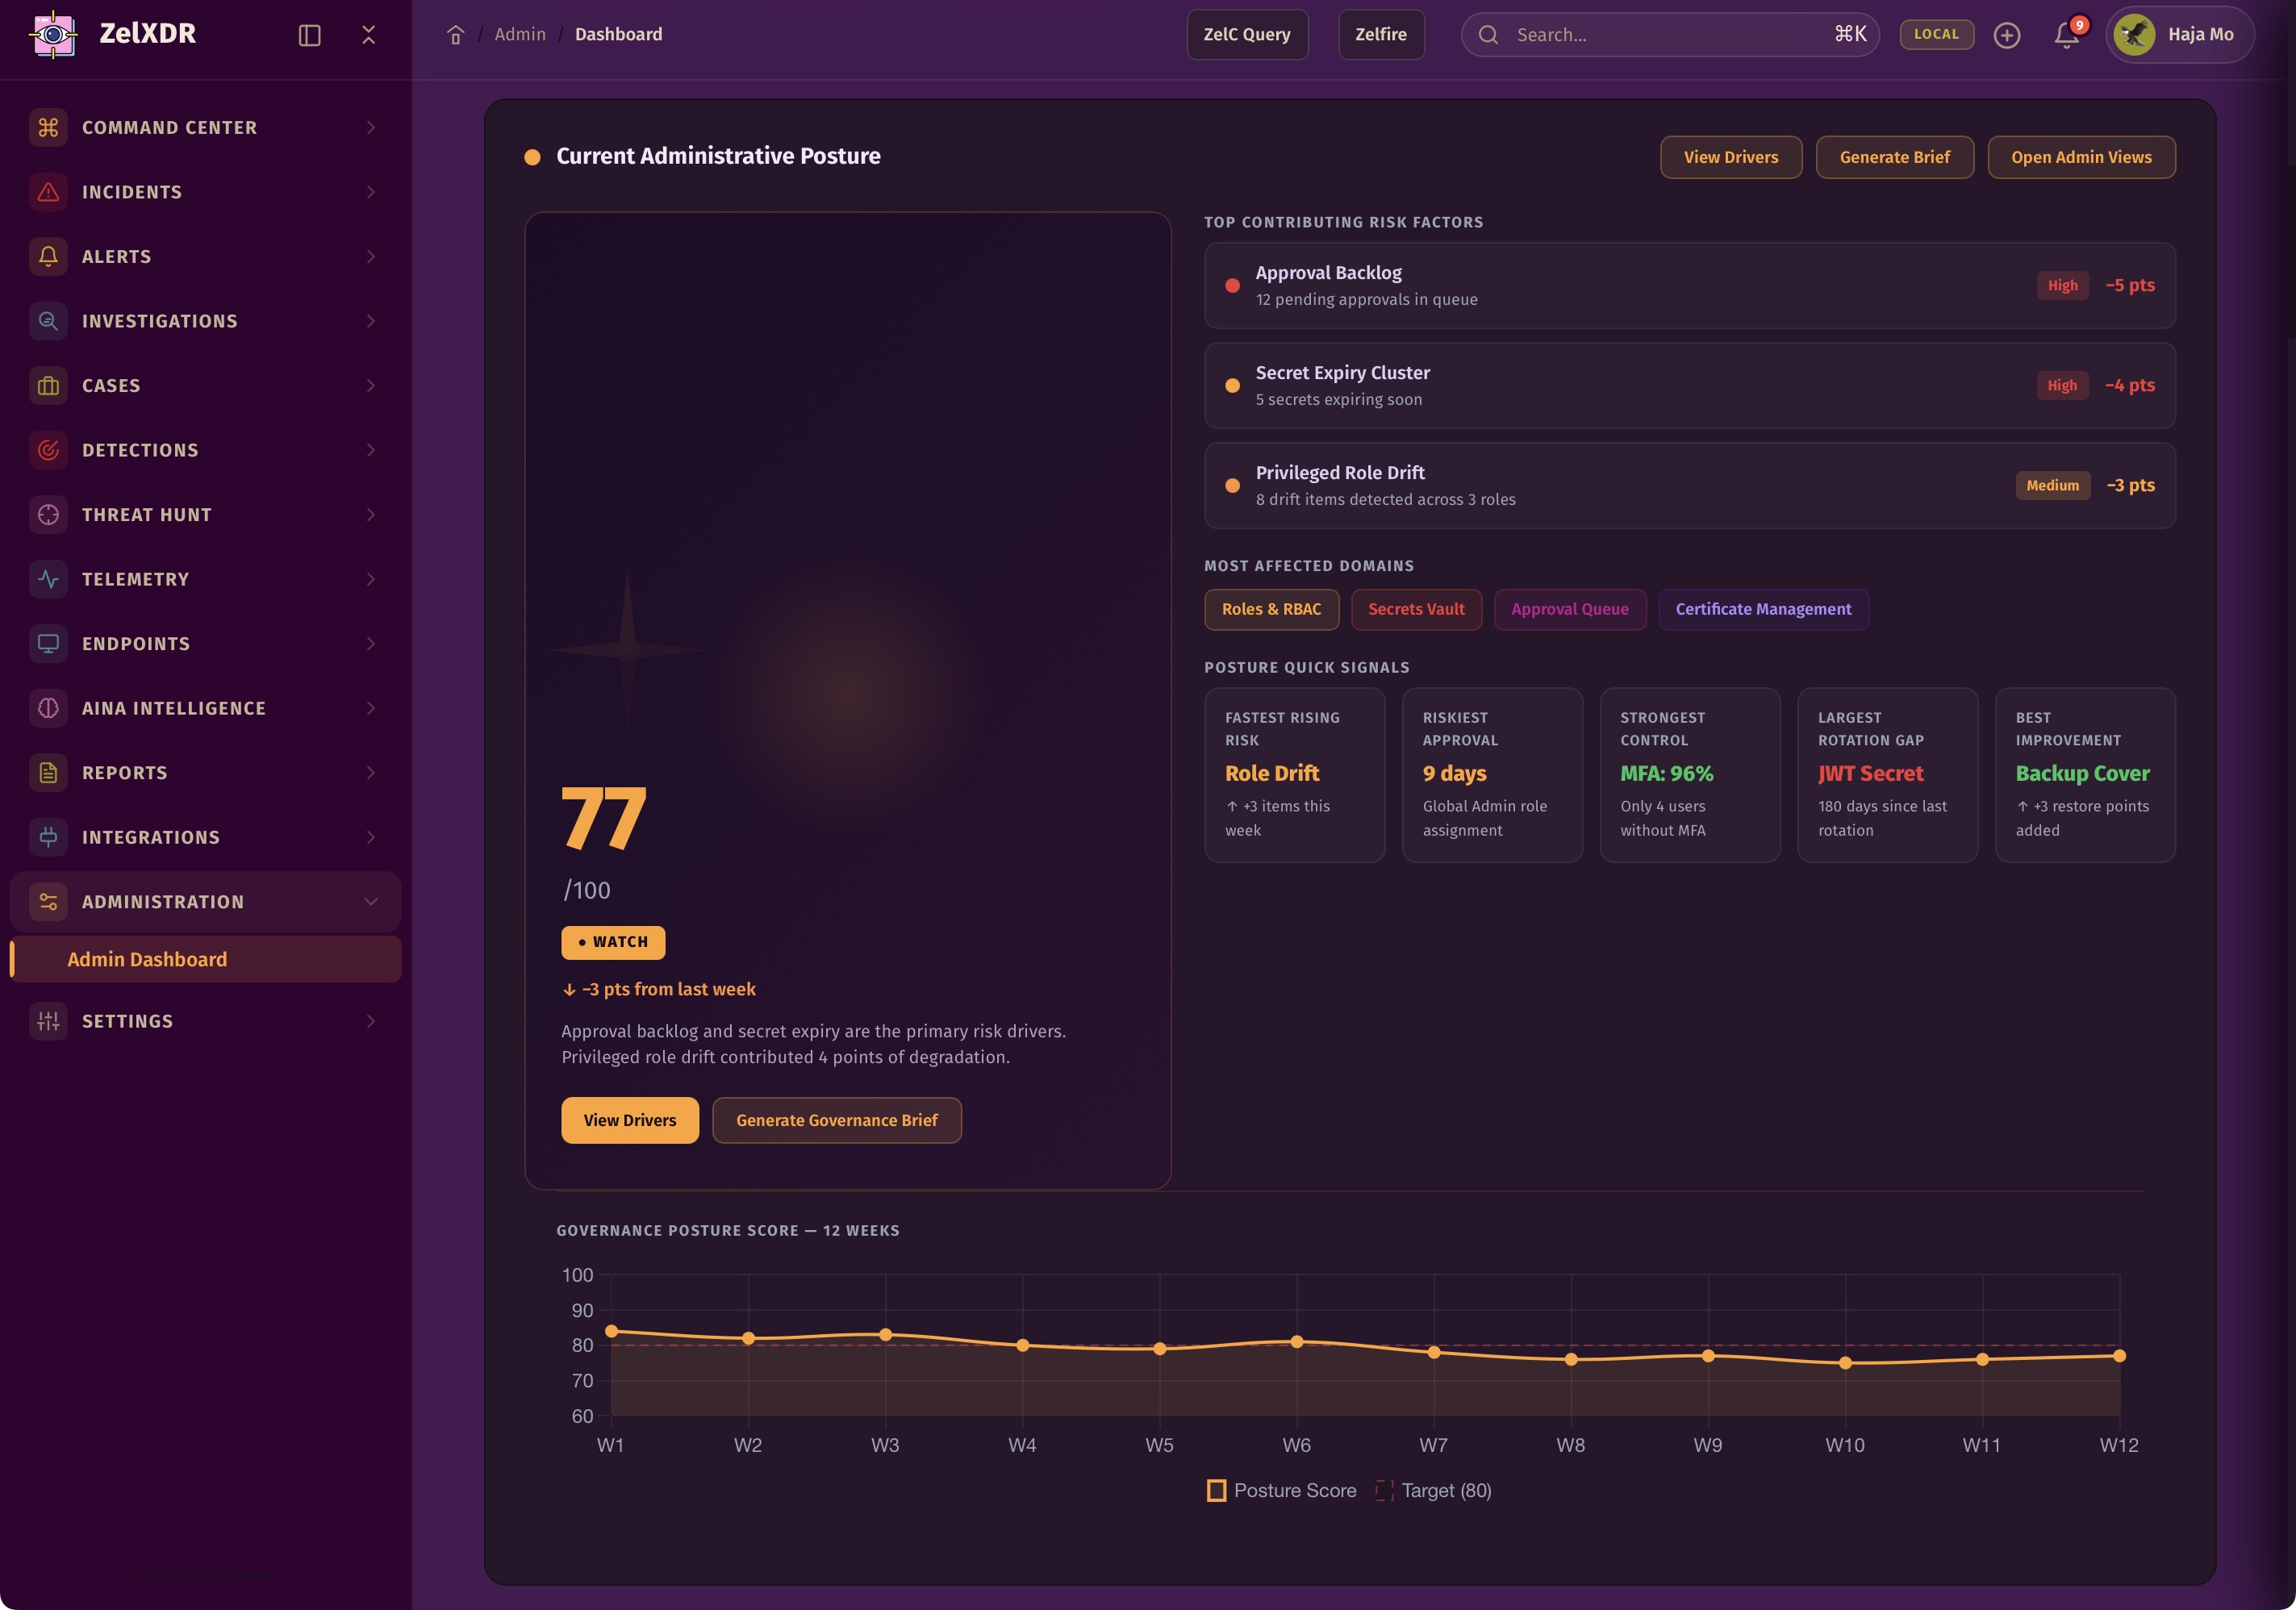
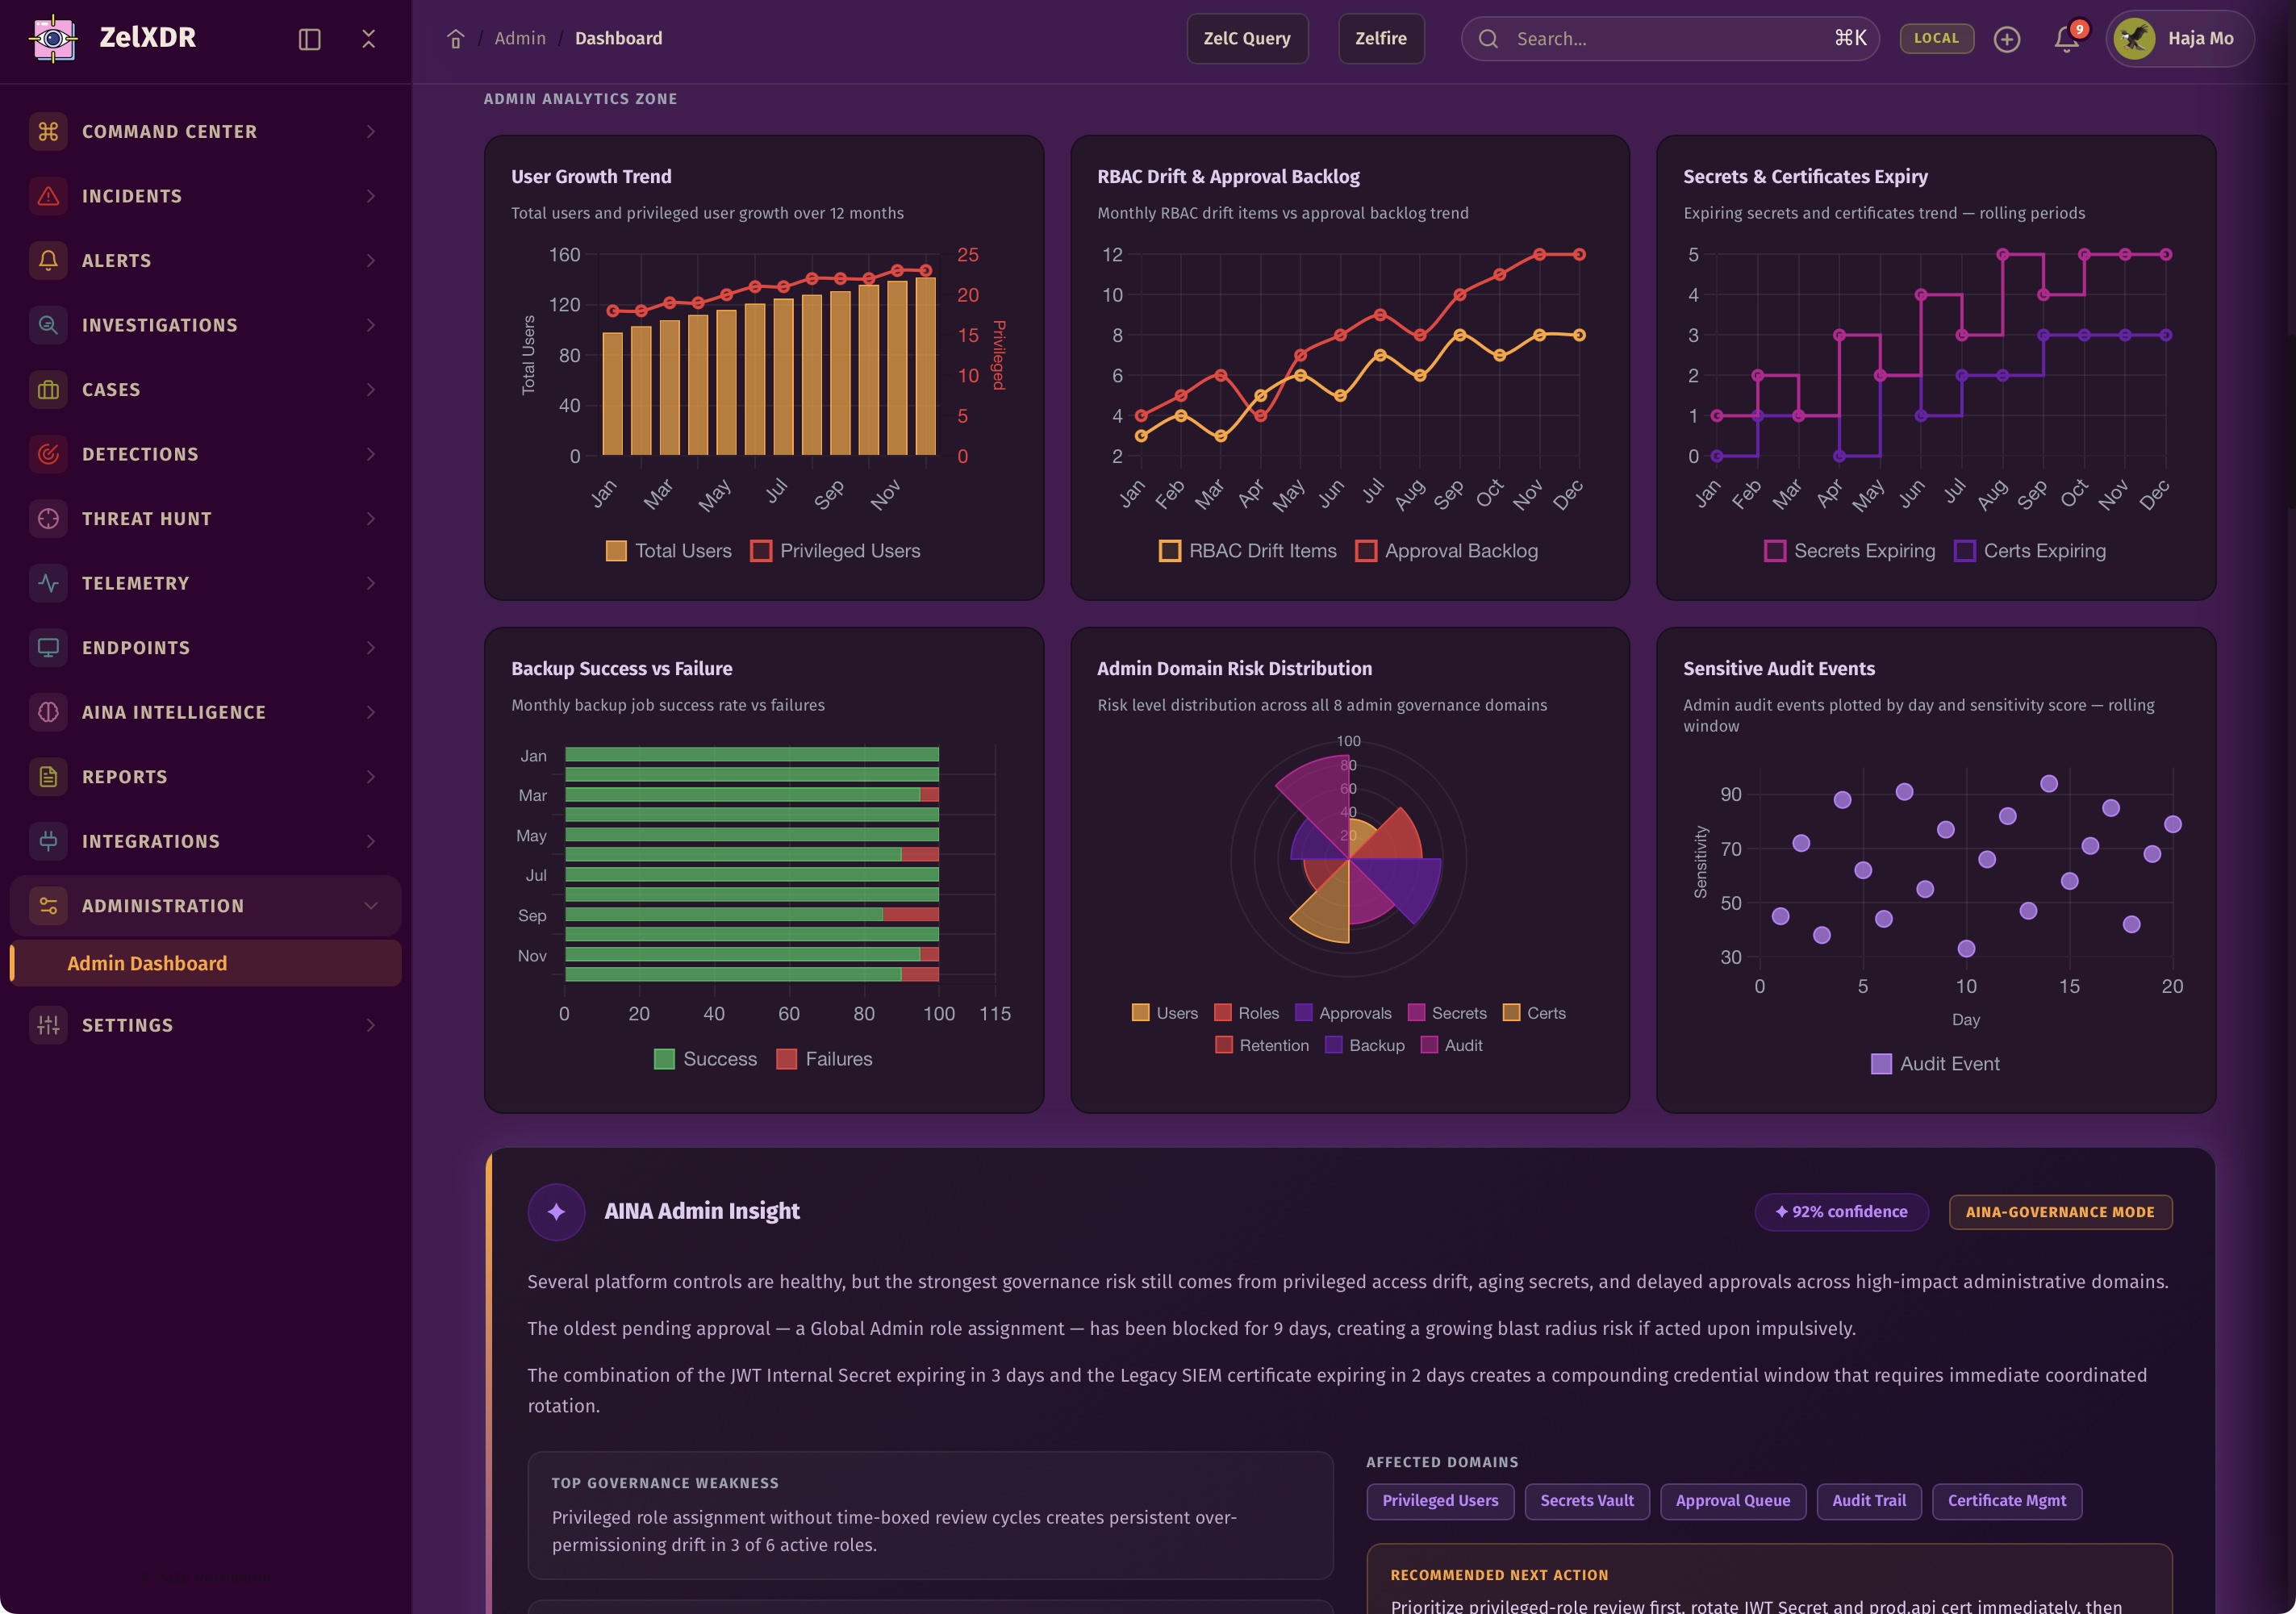
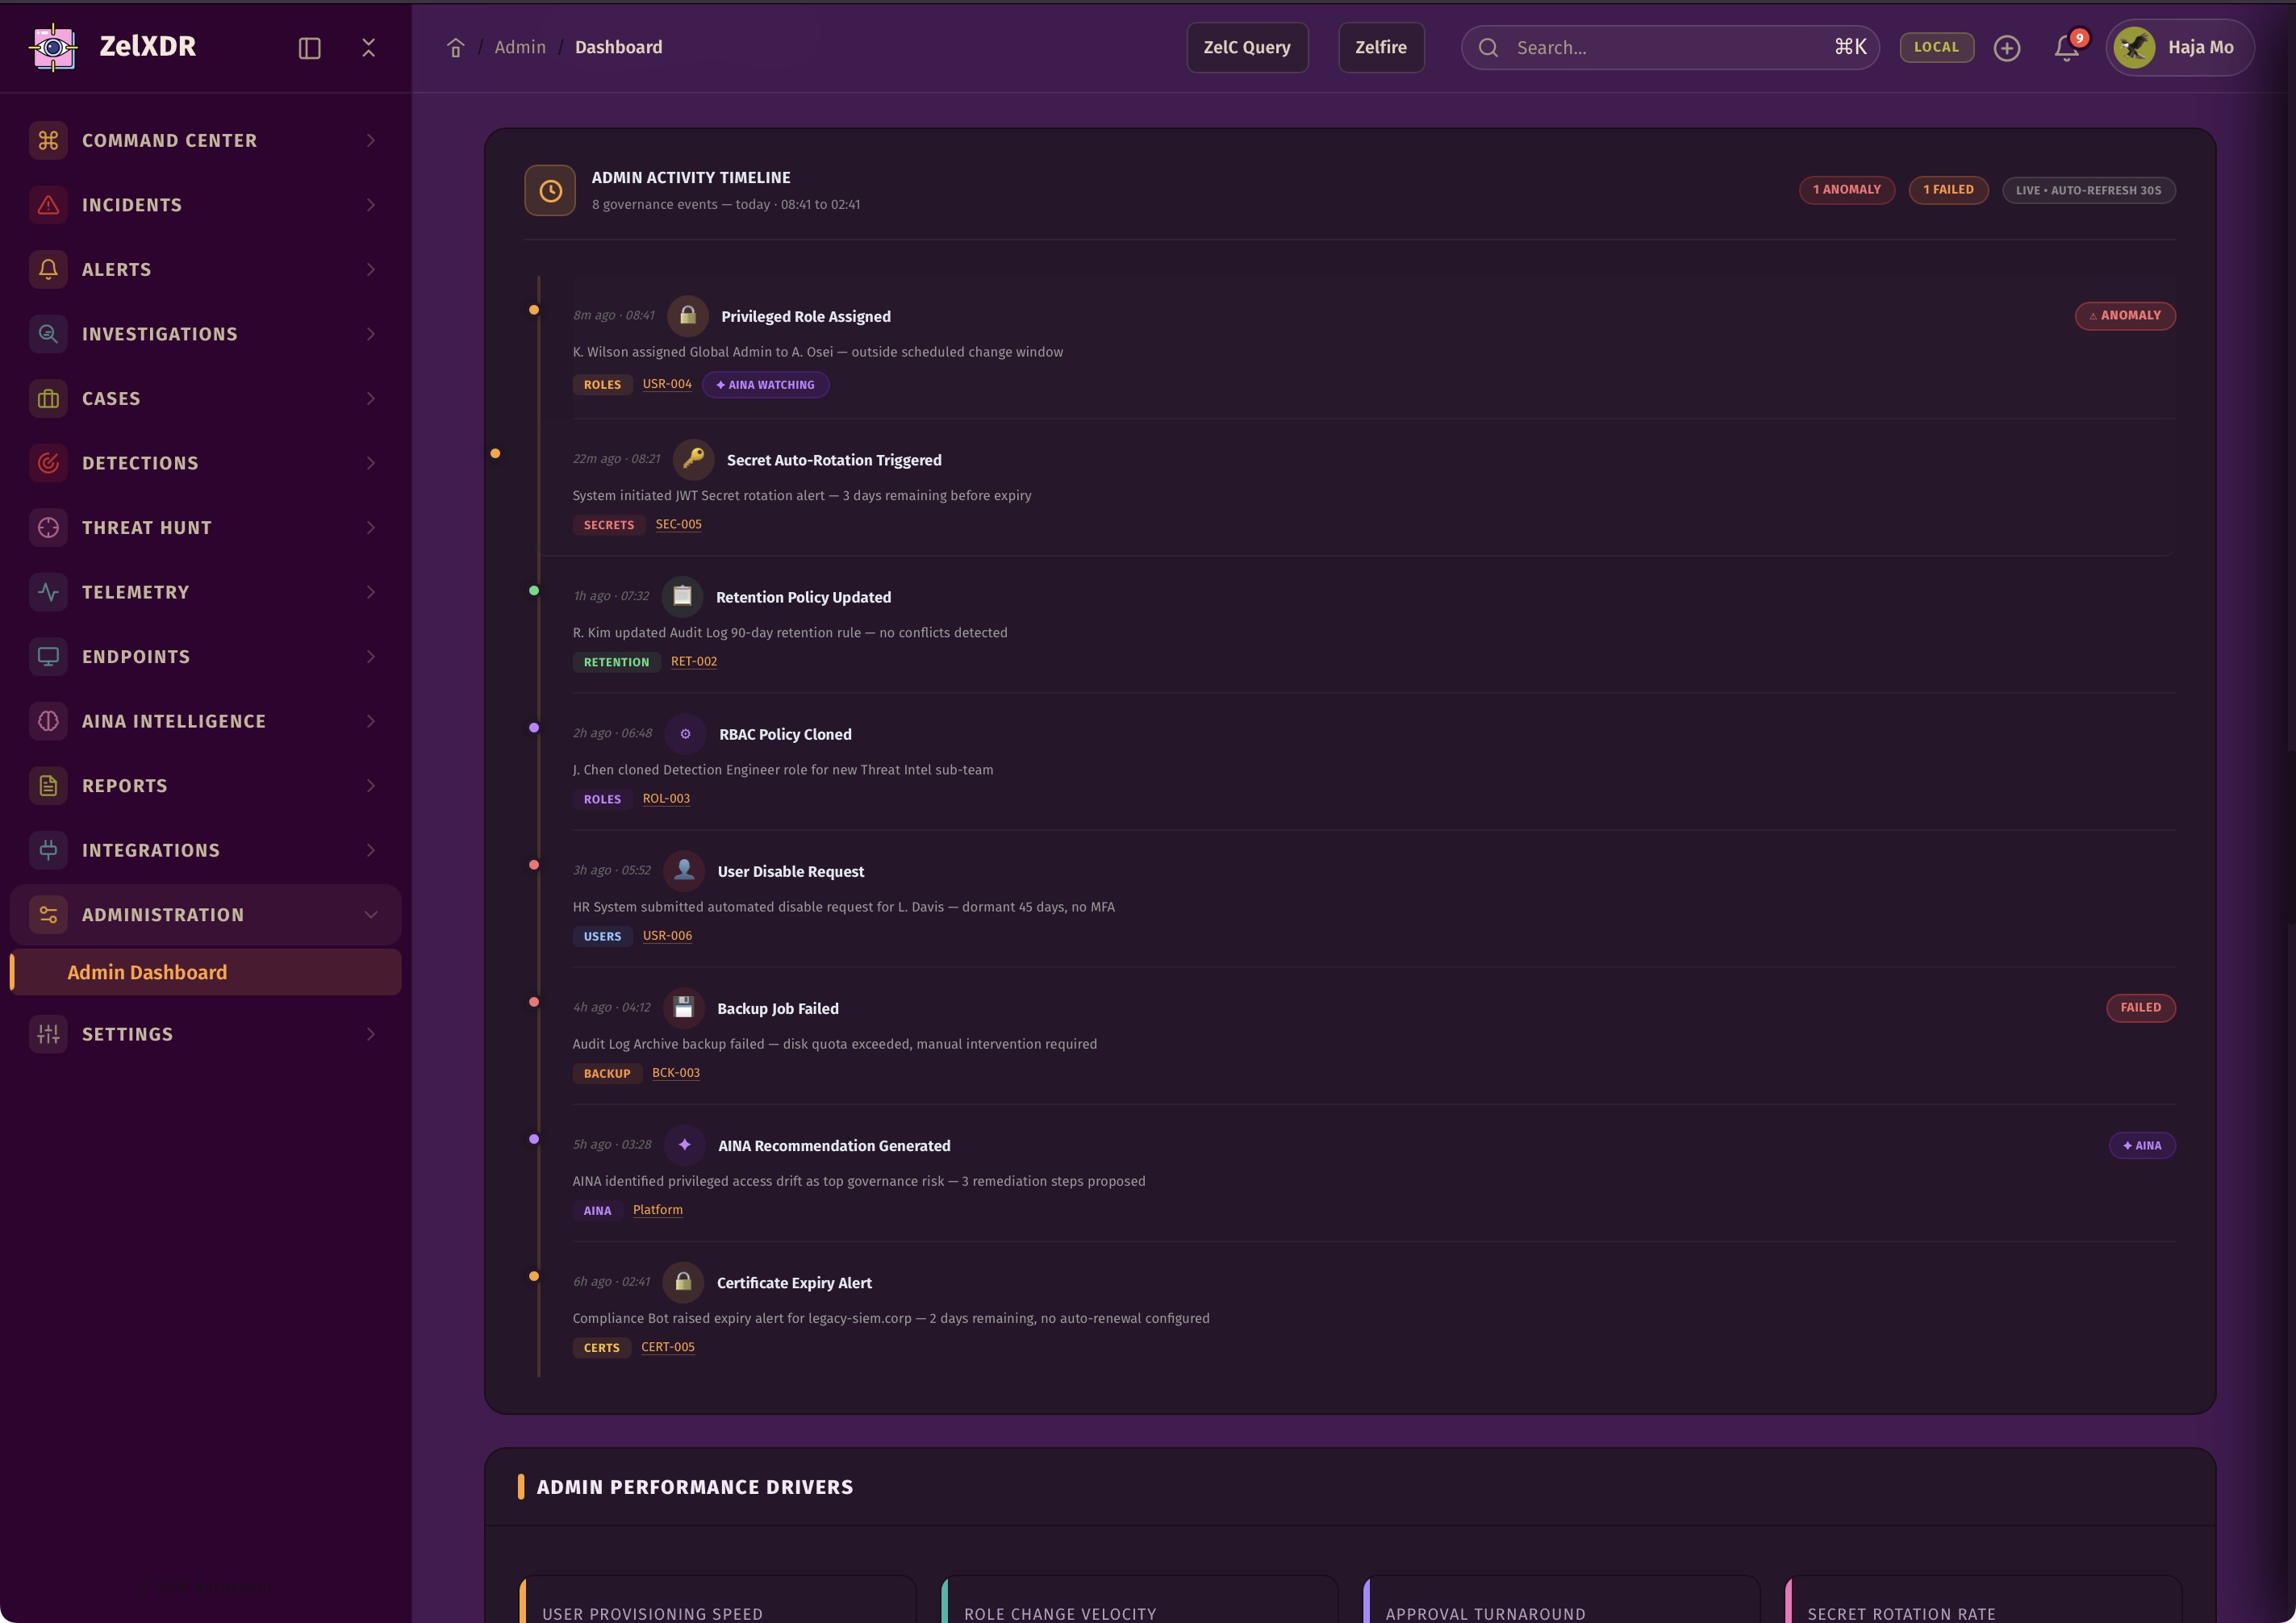
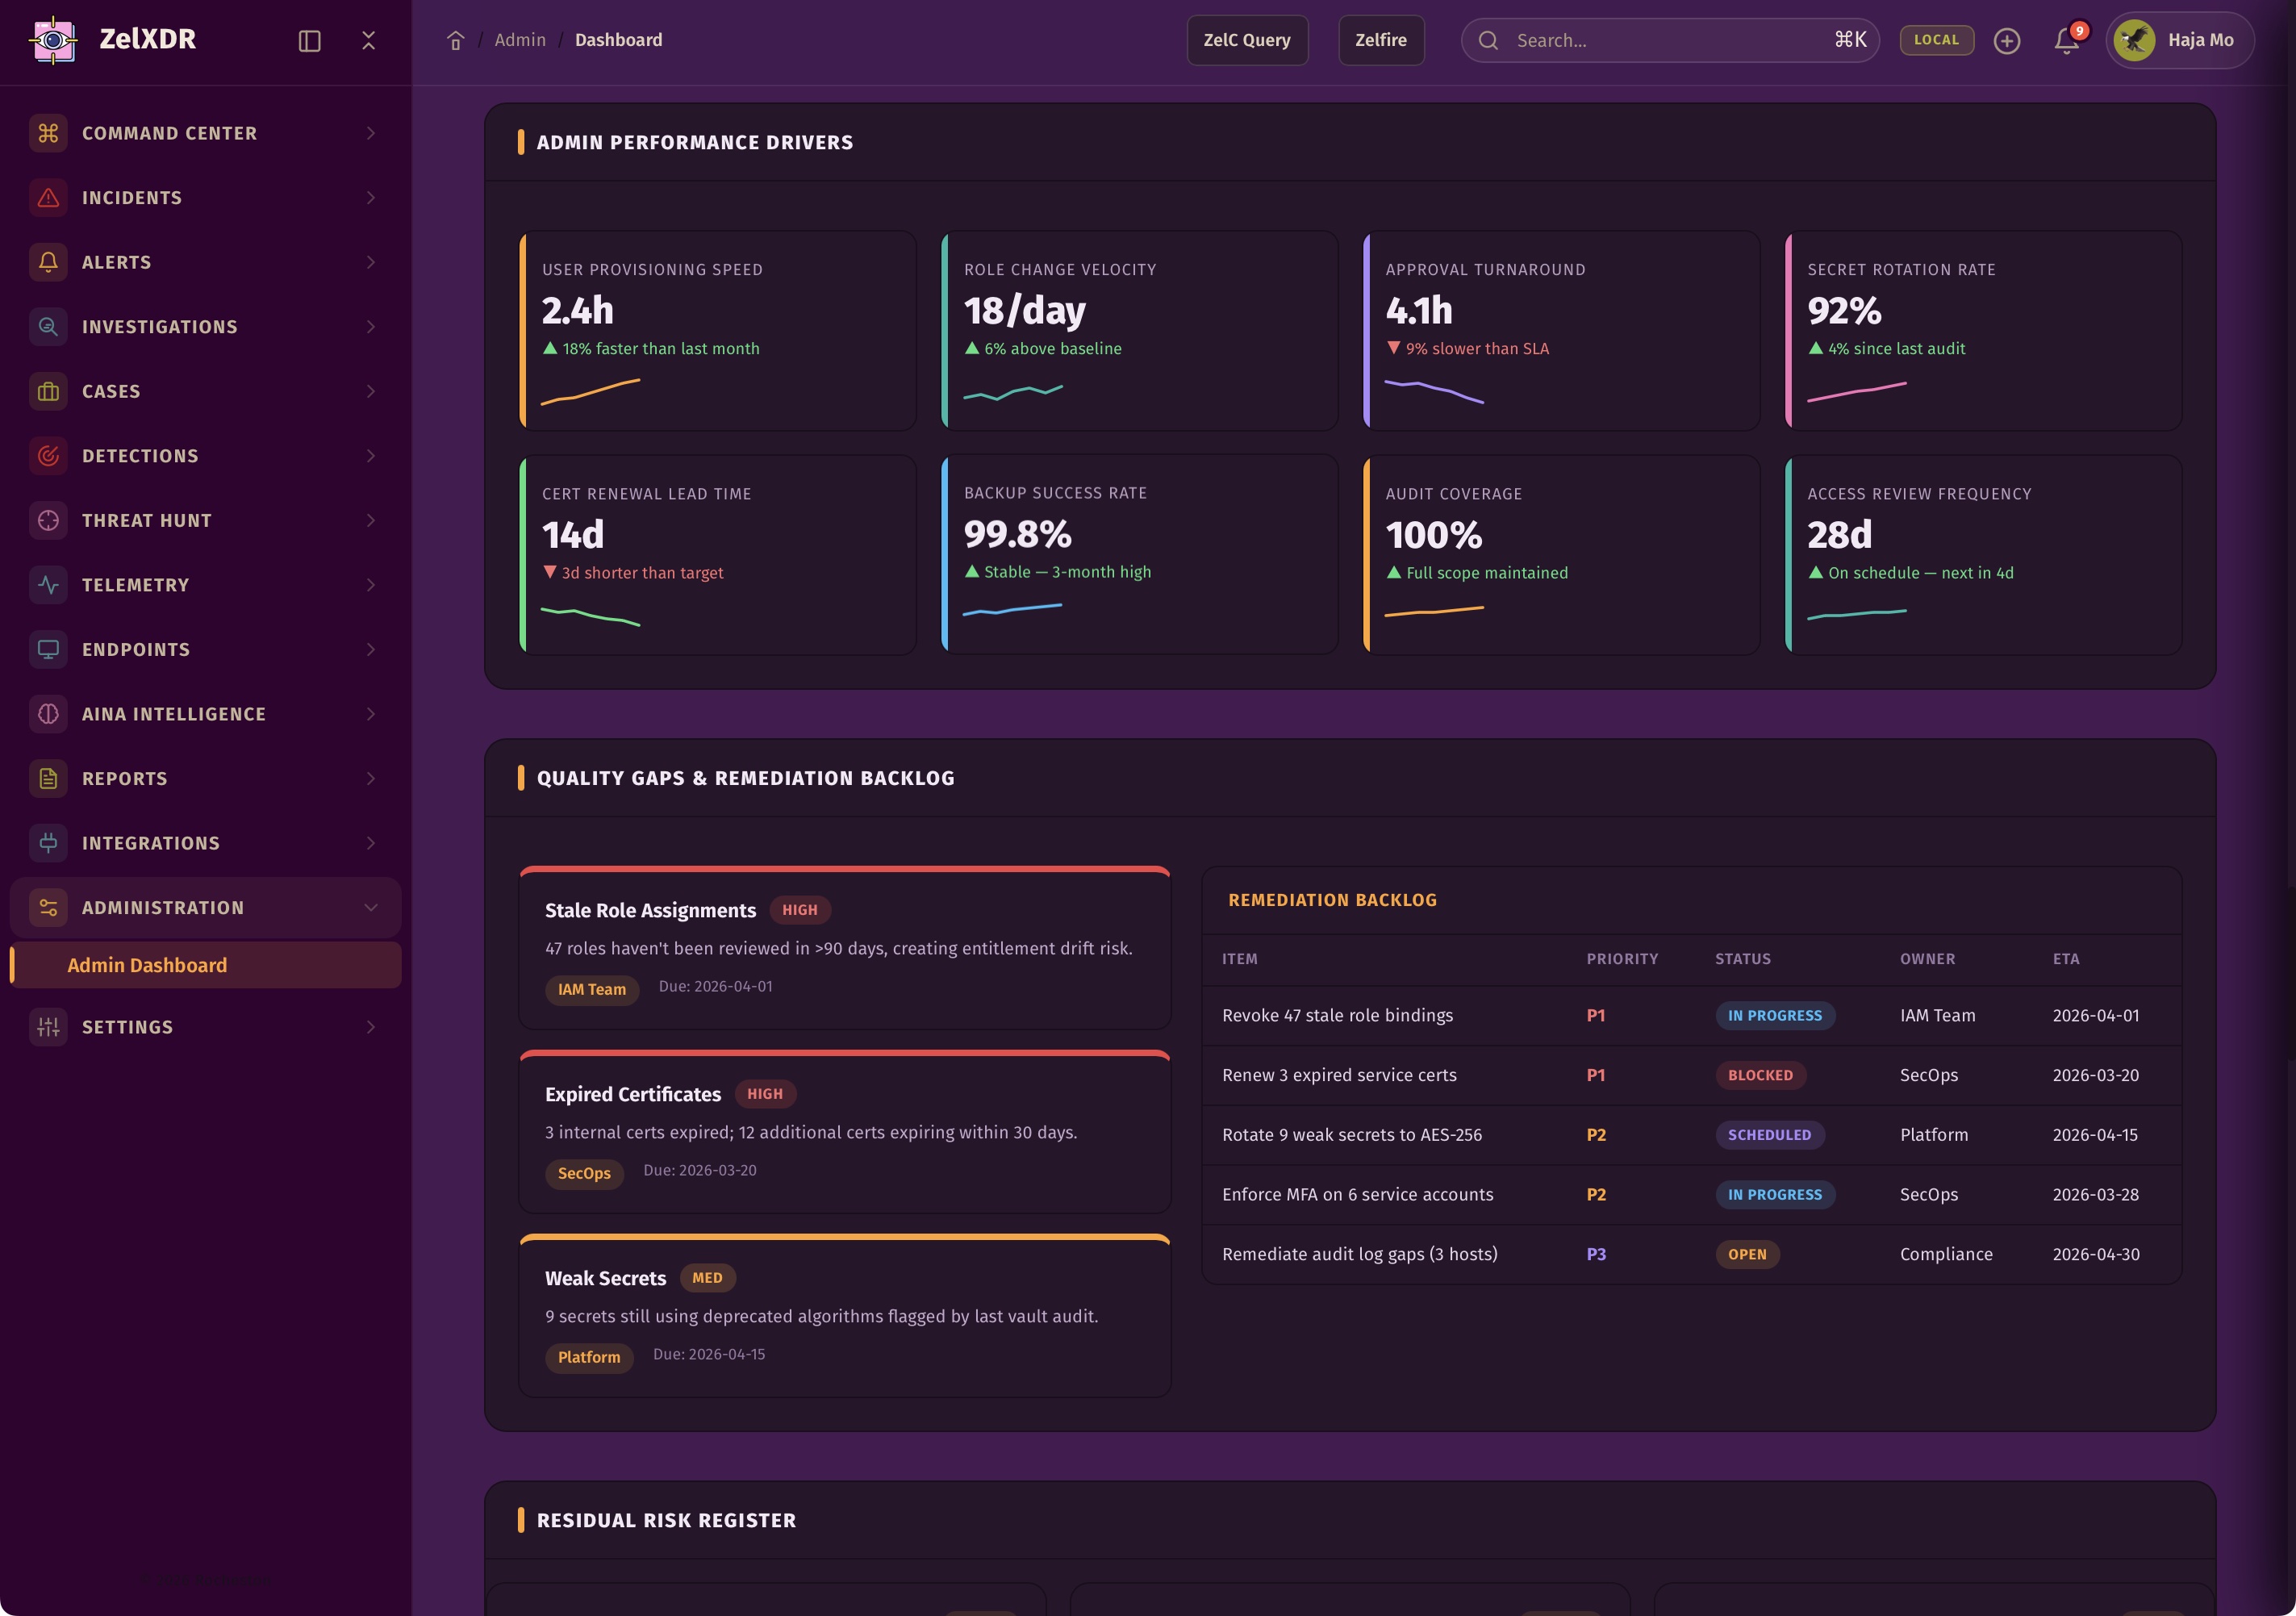
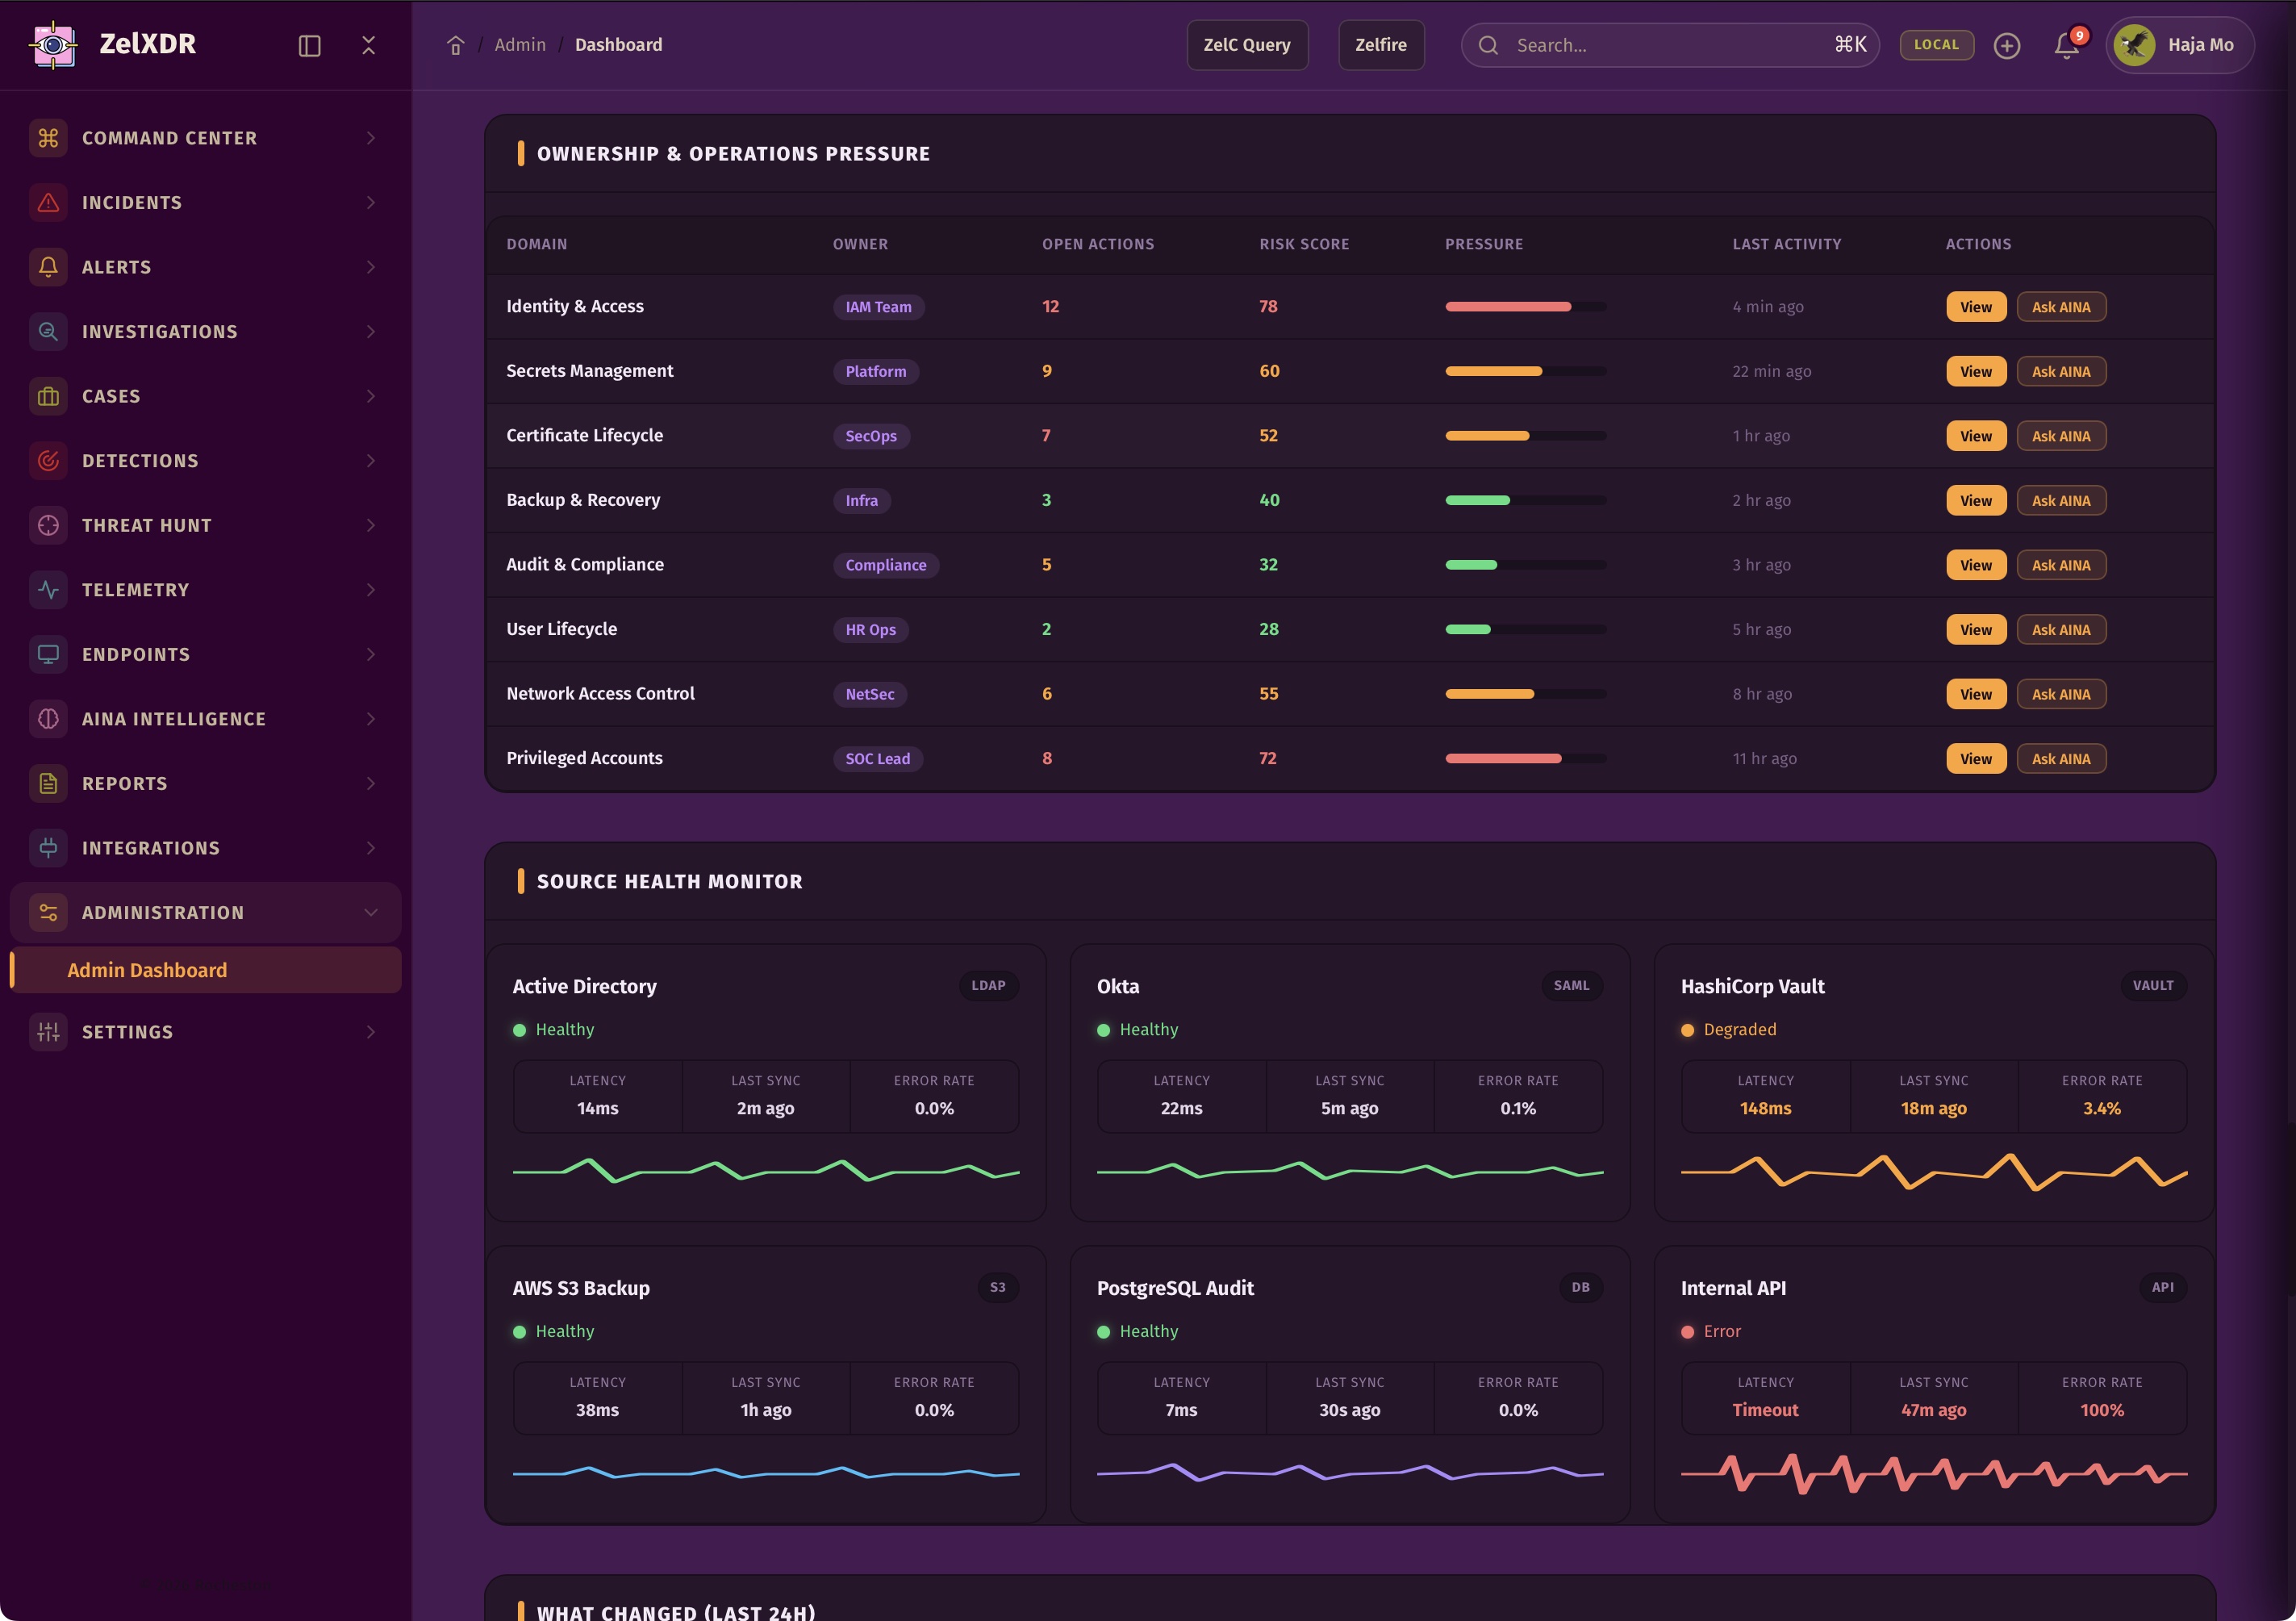
ZelXDR provides strong administrative control across users, roles, approvals, secrets, certificates, backups, retention, labels, teams, and audit logs to keep the platform itself trustworthy.
A secure platform must govern itself as carefully as it governs threats.
From API keys to certificate metadata and rotation pressure, ZelXDR helps teams manage the hidden trust layer that keeps integrations, automation, and AI features operating safely.
Trust fails quietly when secrets are ignored.
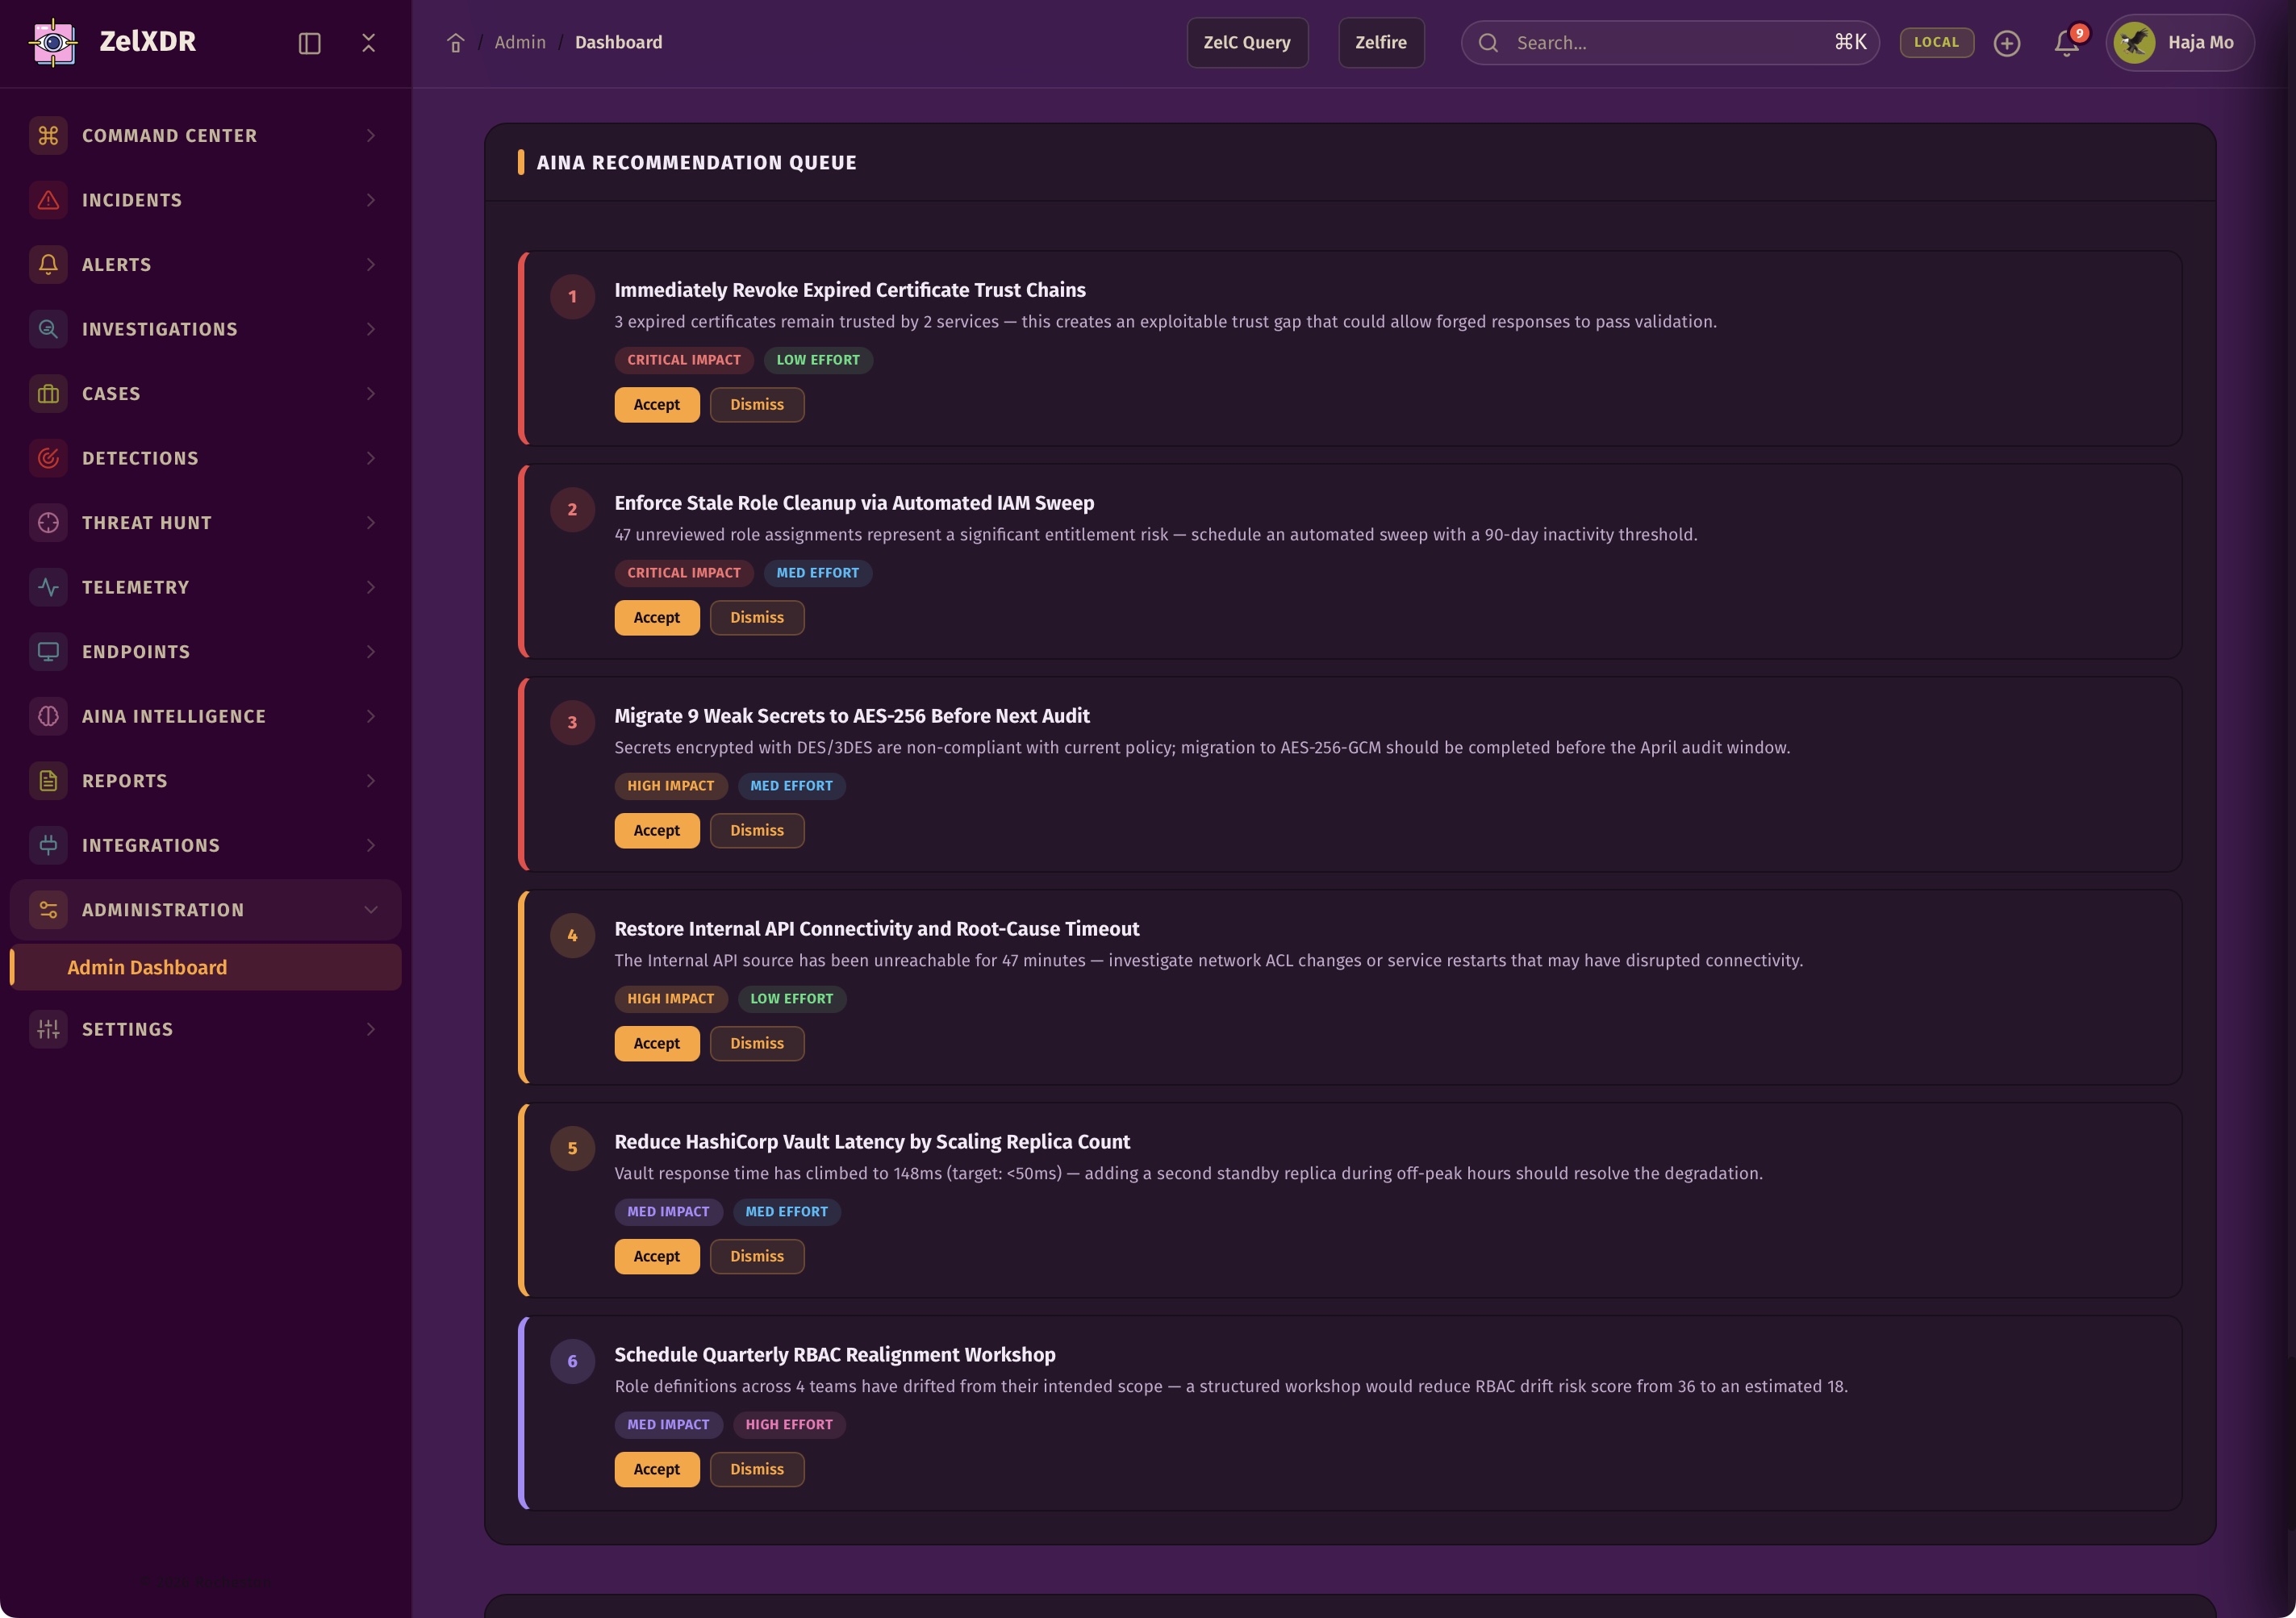
AINA assists with triage, incident understanding, root-cause thinking, executive summaries, next-step recommendations, and business-impact reasoning across the platform.
AI is strongest when it helps humans decide better.
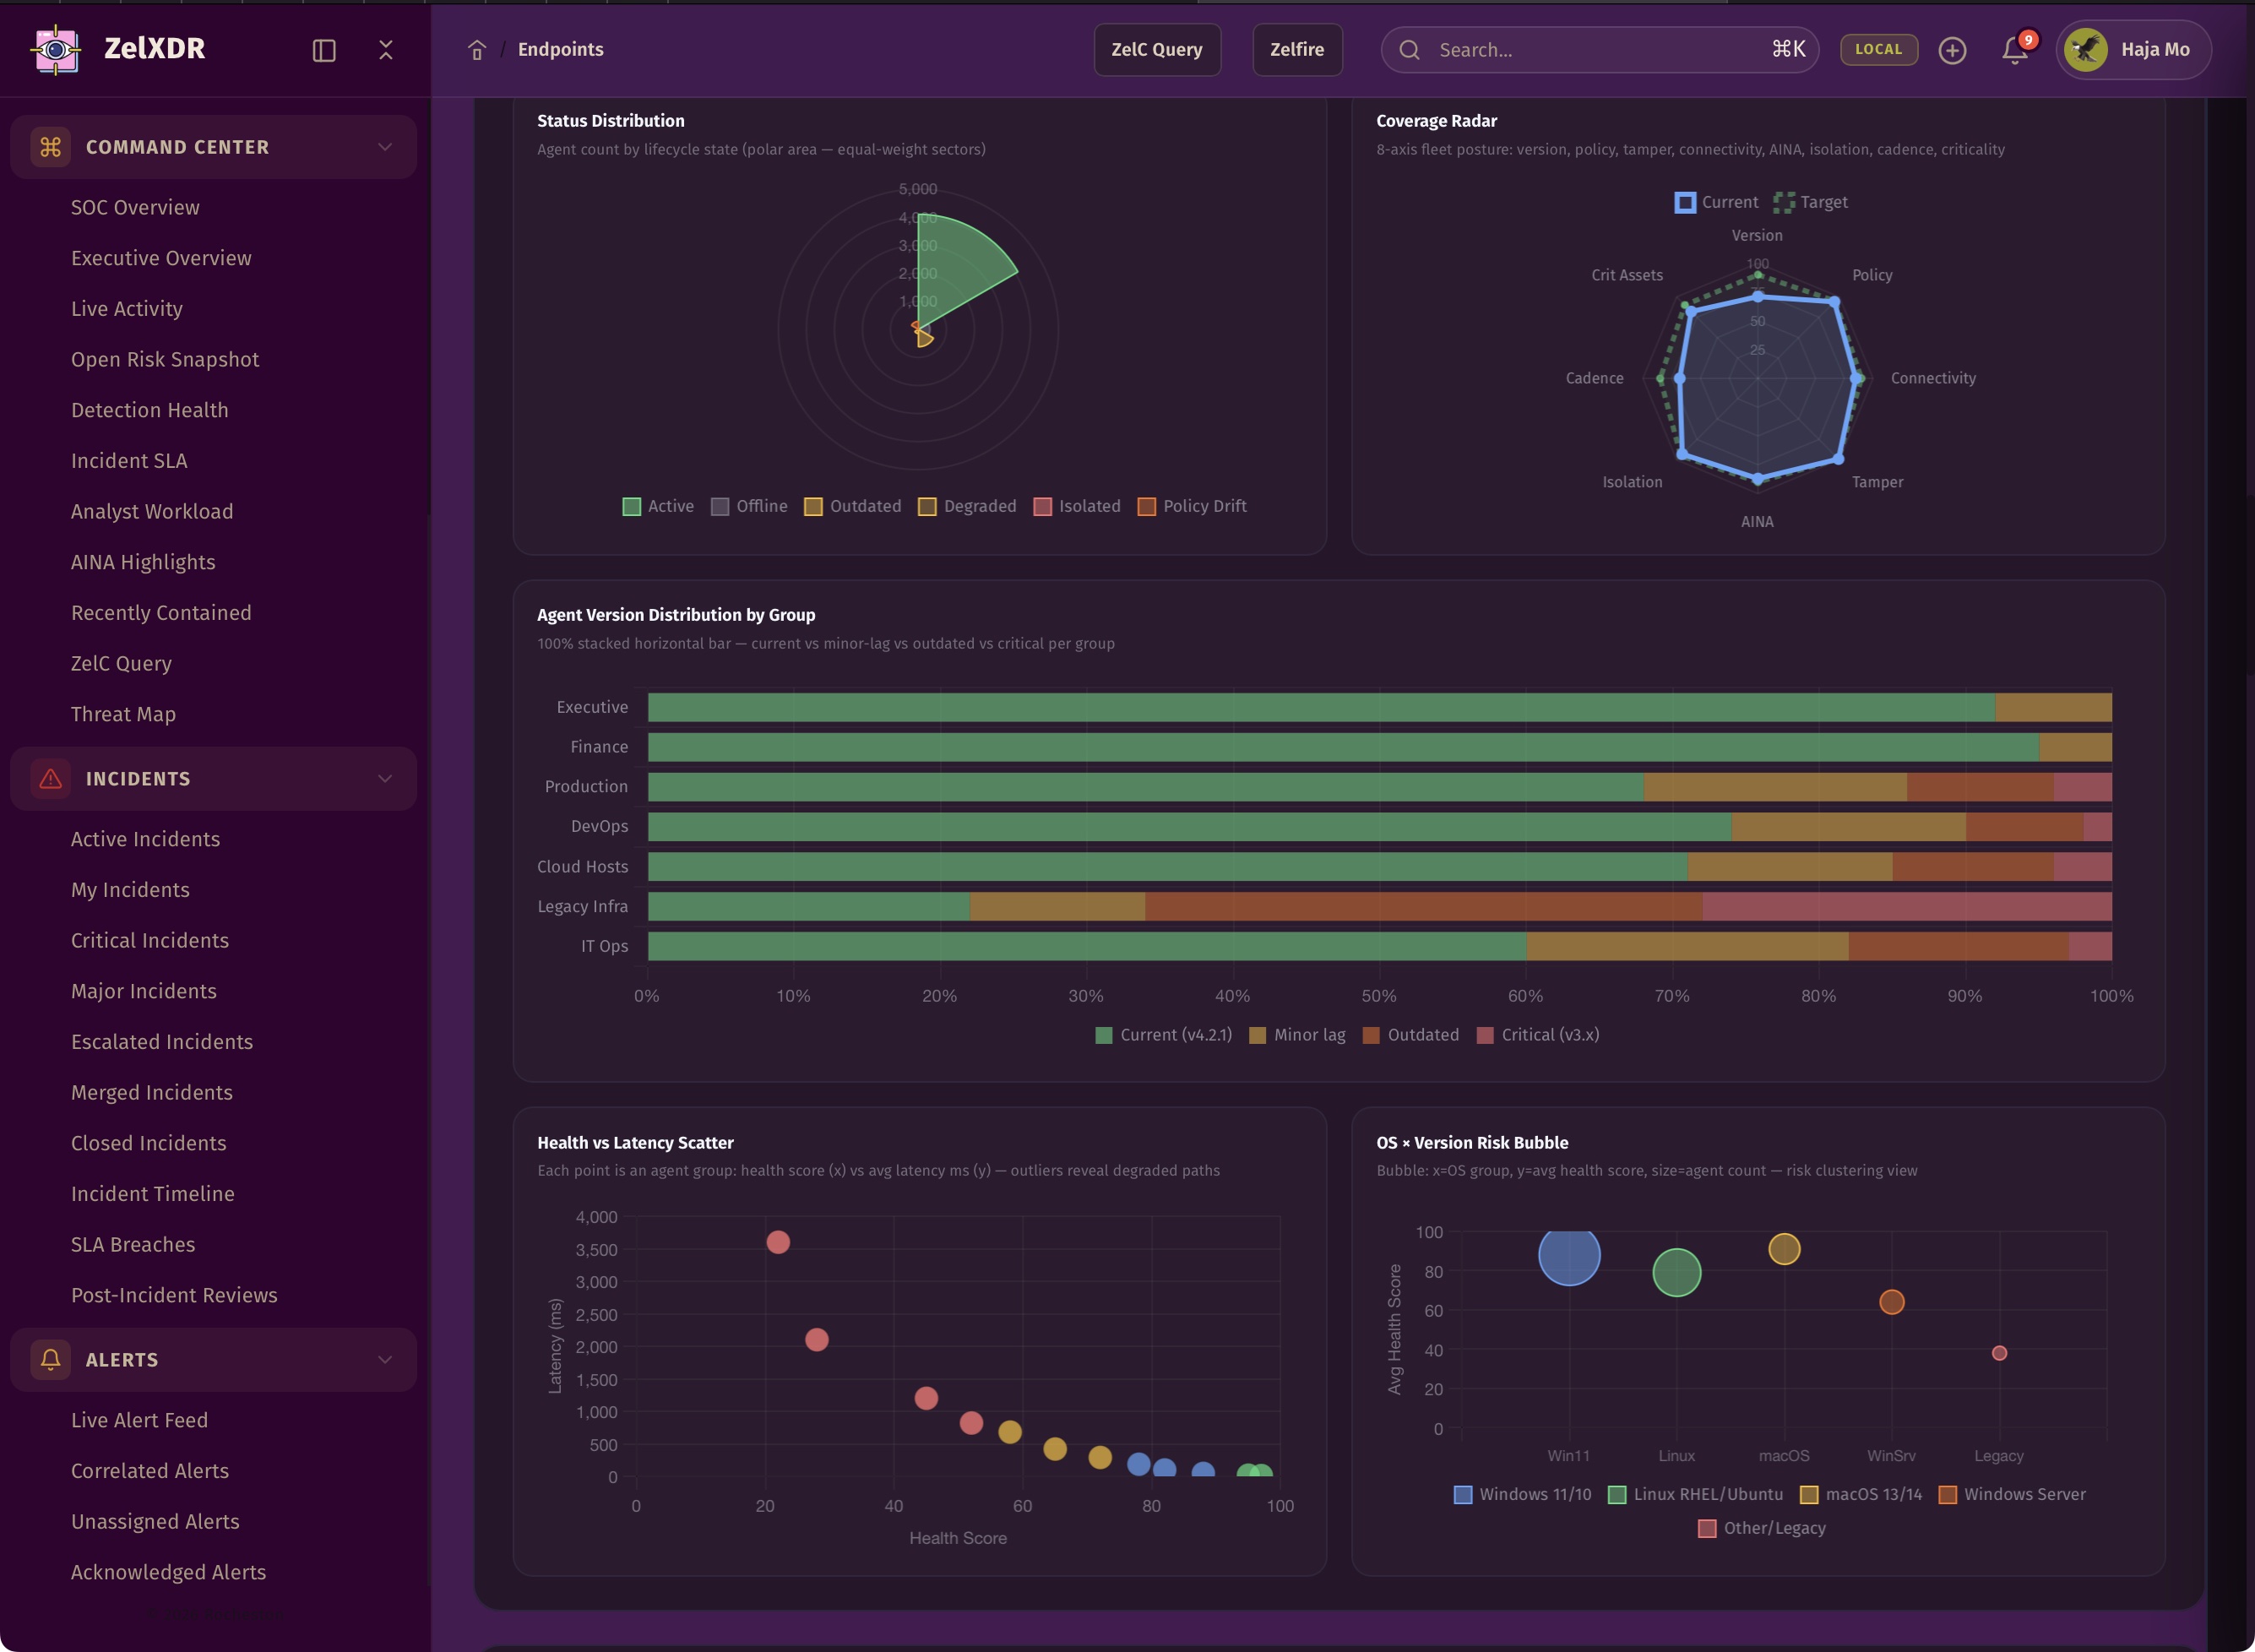
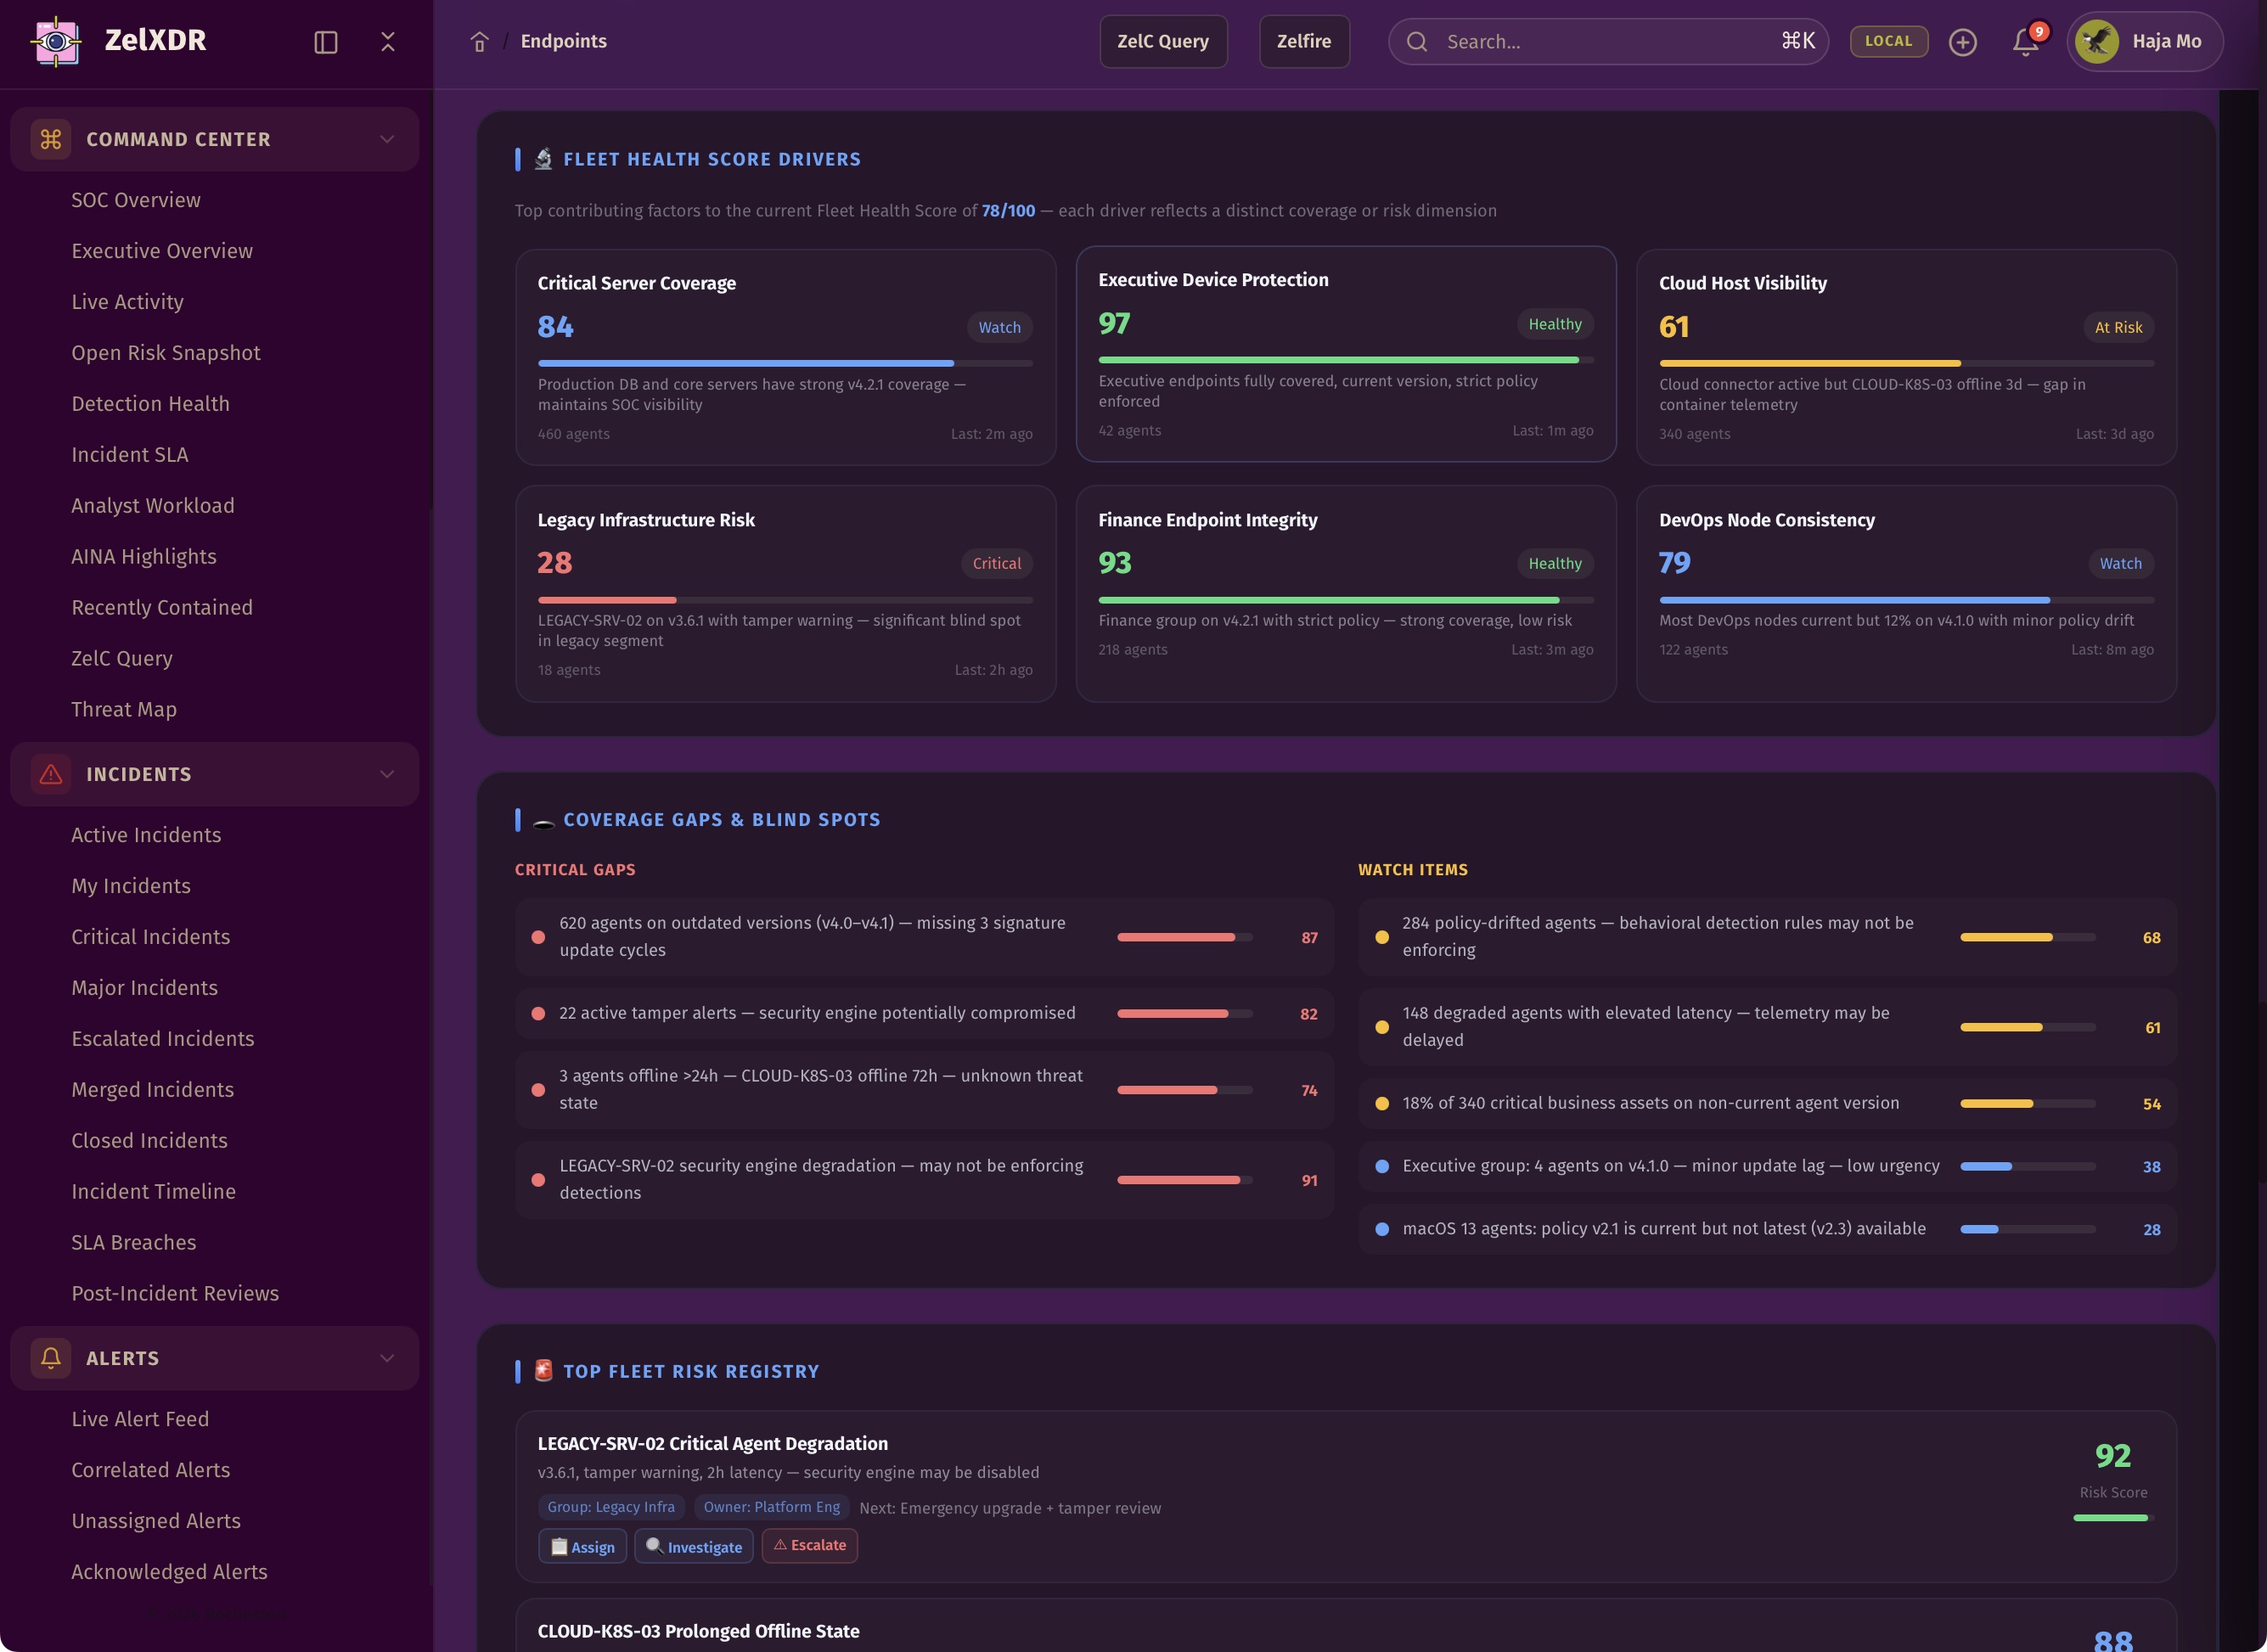
ZelXDR gives teams visibility into endpoint health, agent status, isolation state, policy drift, version lag, and fleet-wide operational risk across critical business groups.
A healthy fleet is the foundation of reliable defense.
ZelXDR is not a static dashboard. It is a growing operational fabric that can expand across detections, workflows, AI reasoning, integrations, reports, hunts, and governance as security demands evolve.
Defense is not static, and the platform should not be either.
UNDER THE HOOD
Architecture, integrations, security controls, and operational details for ZelXDR.
INSIDE ZELXDR
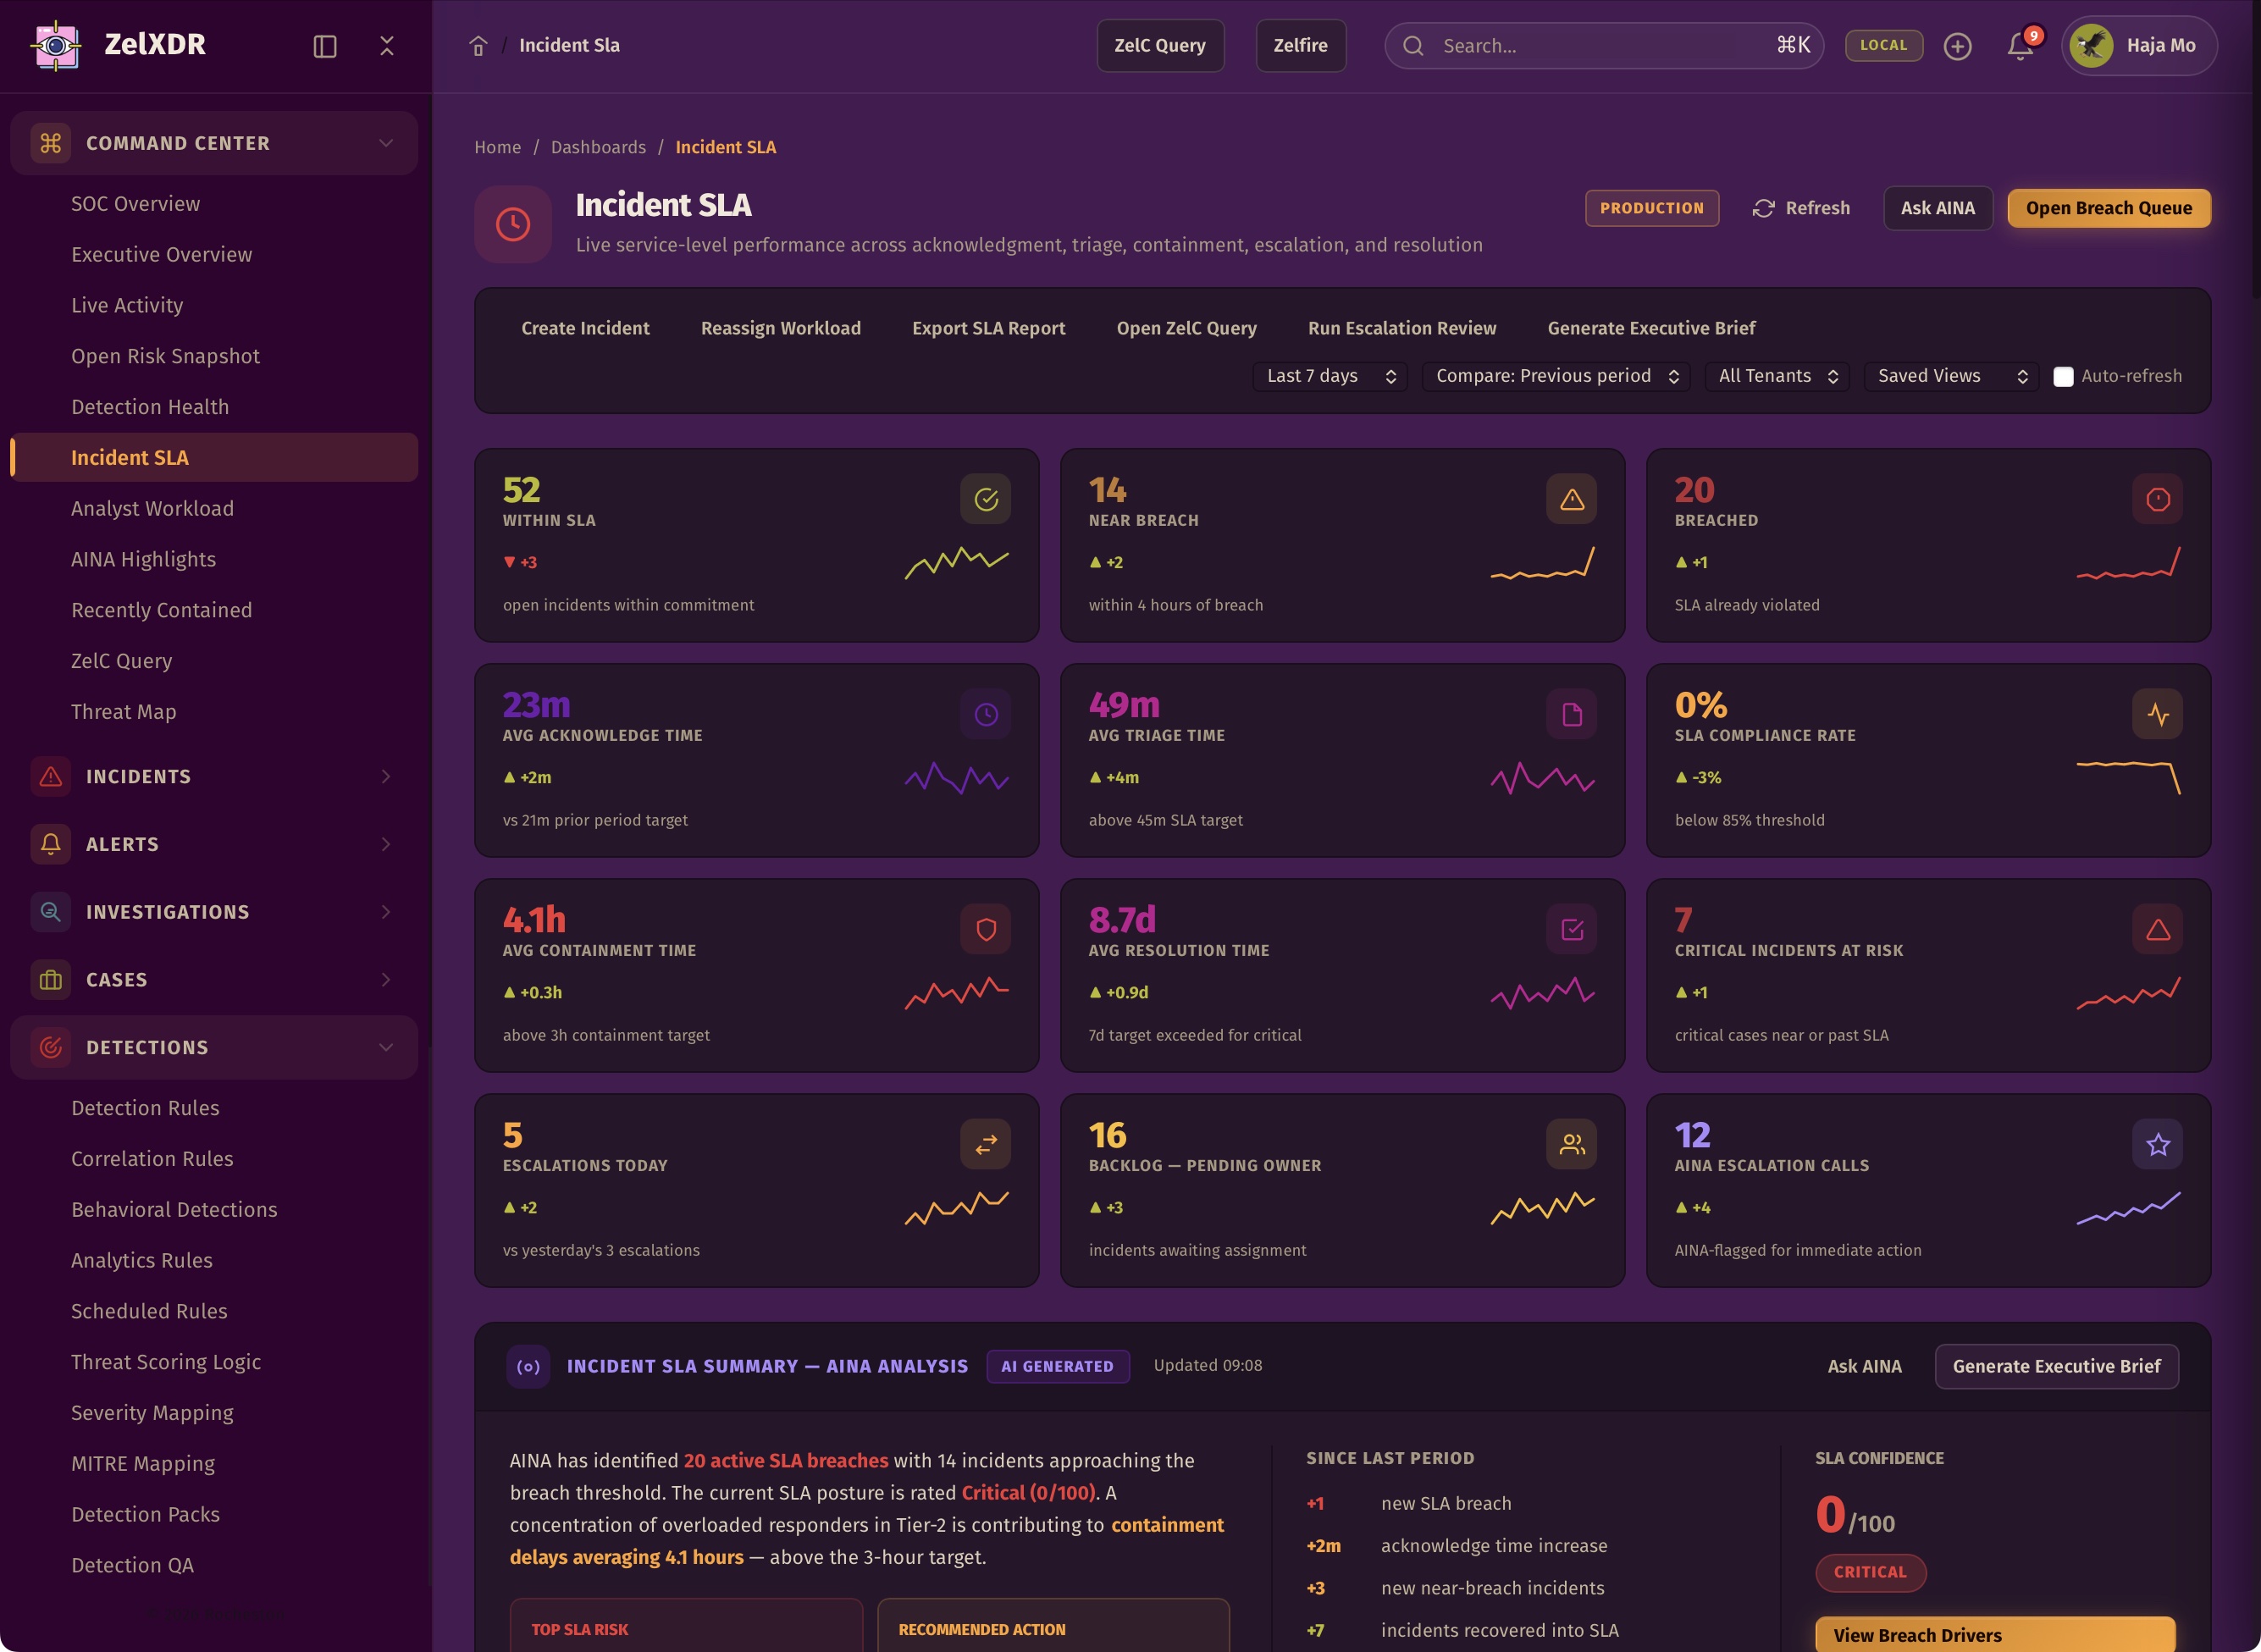
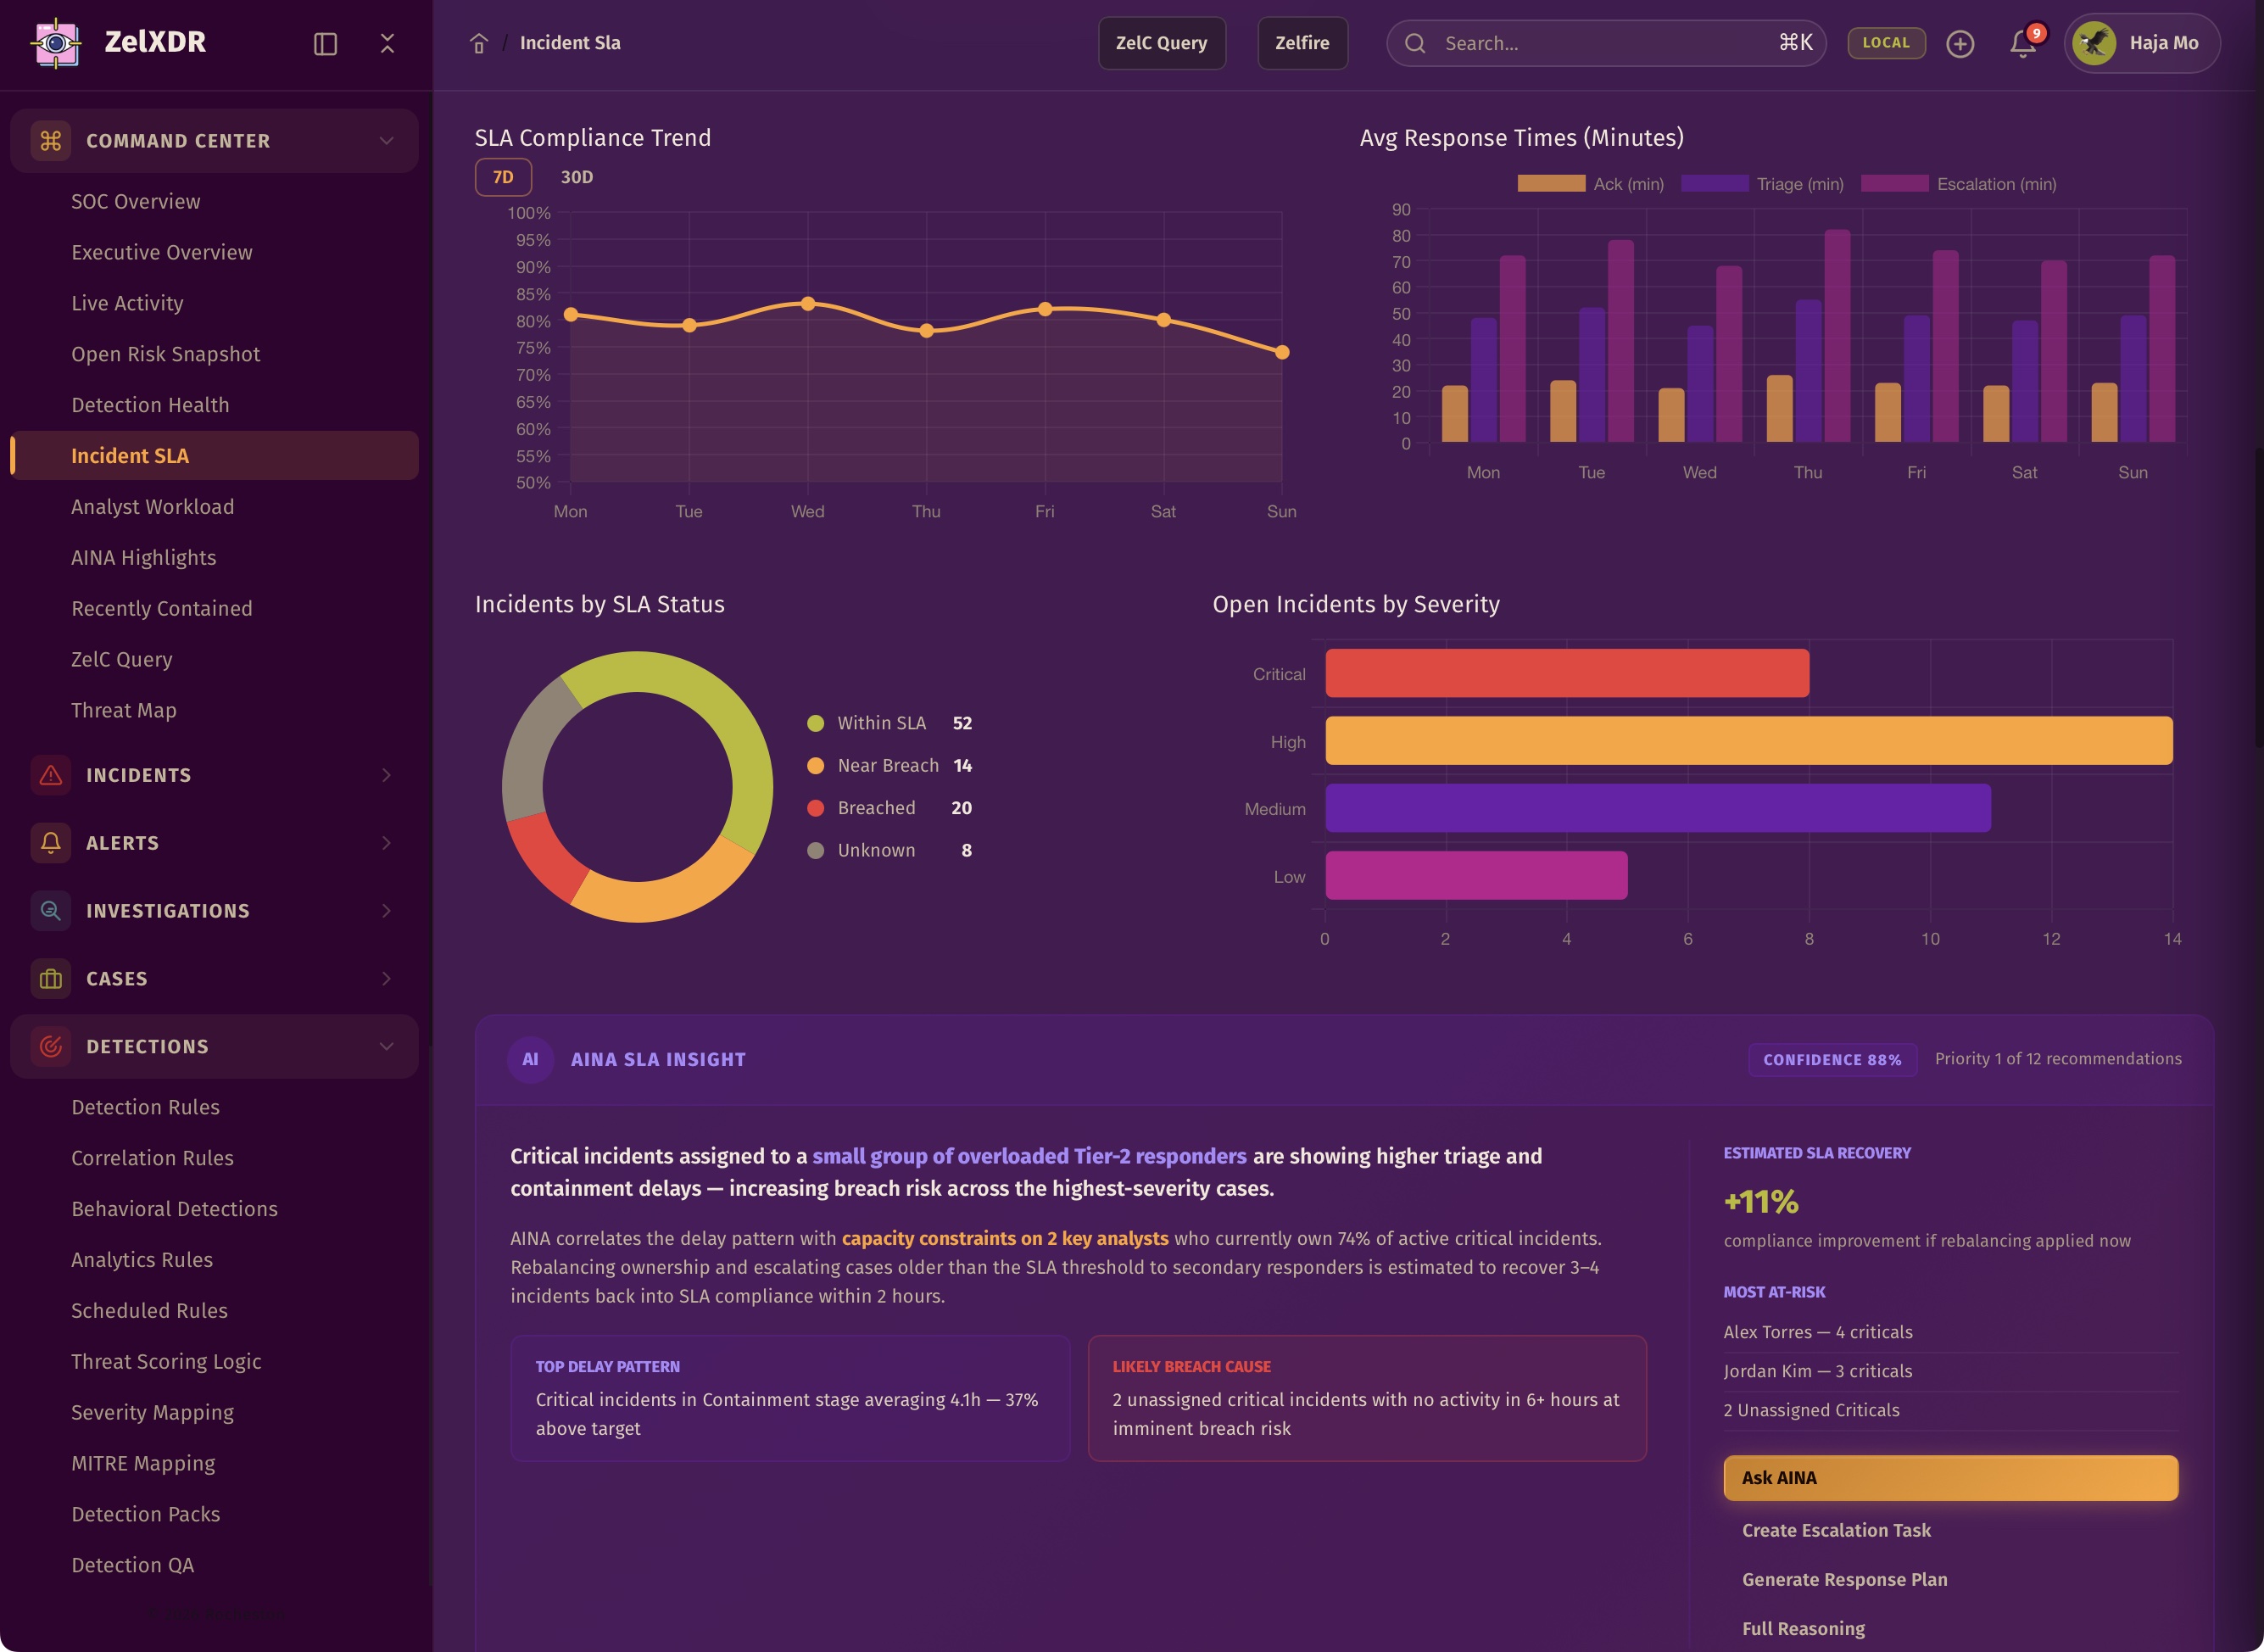
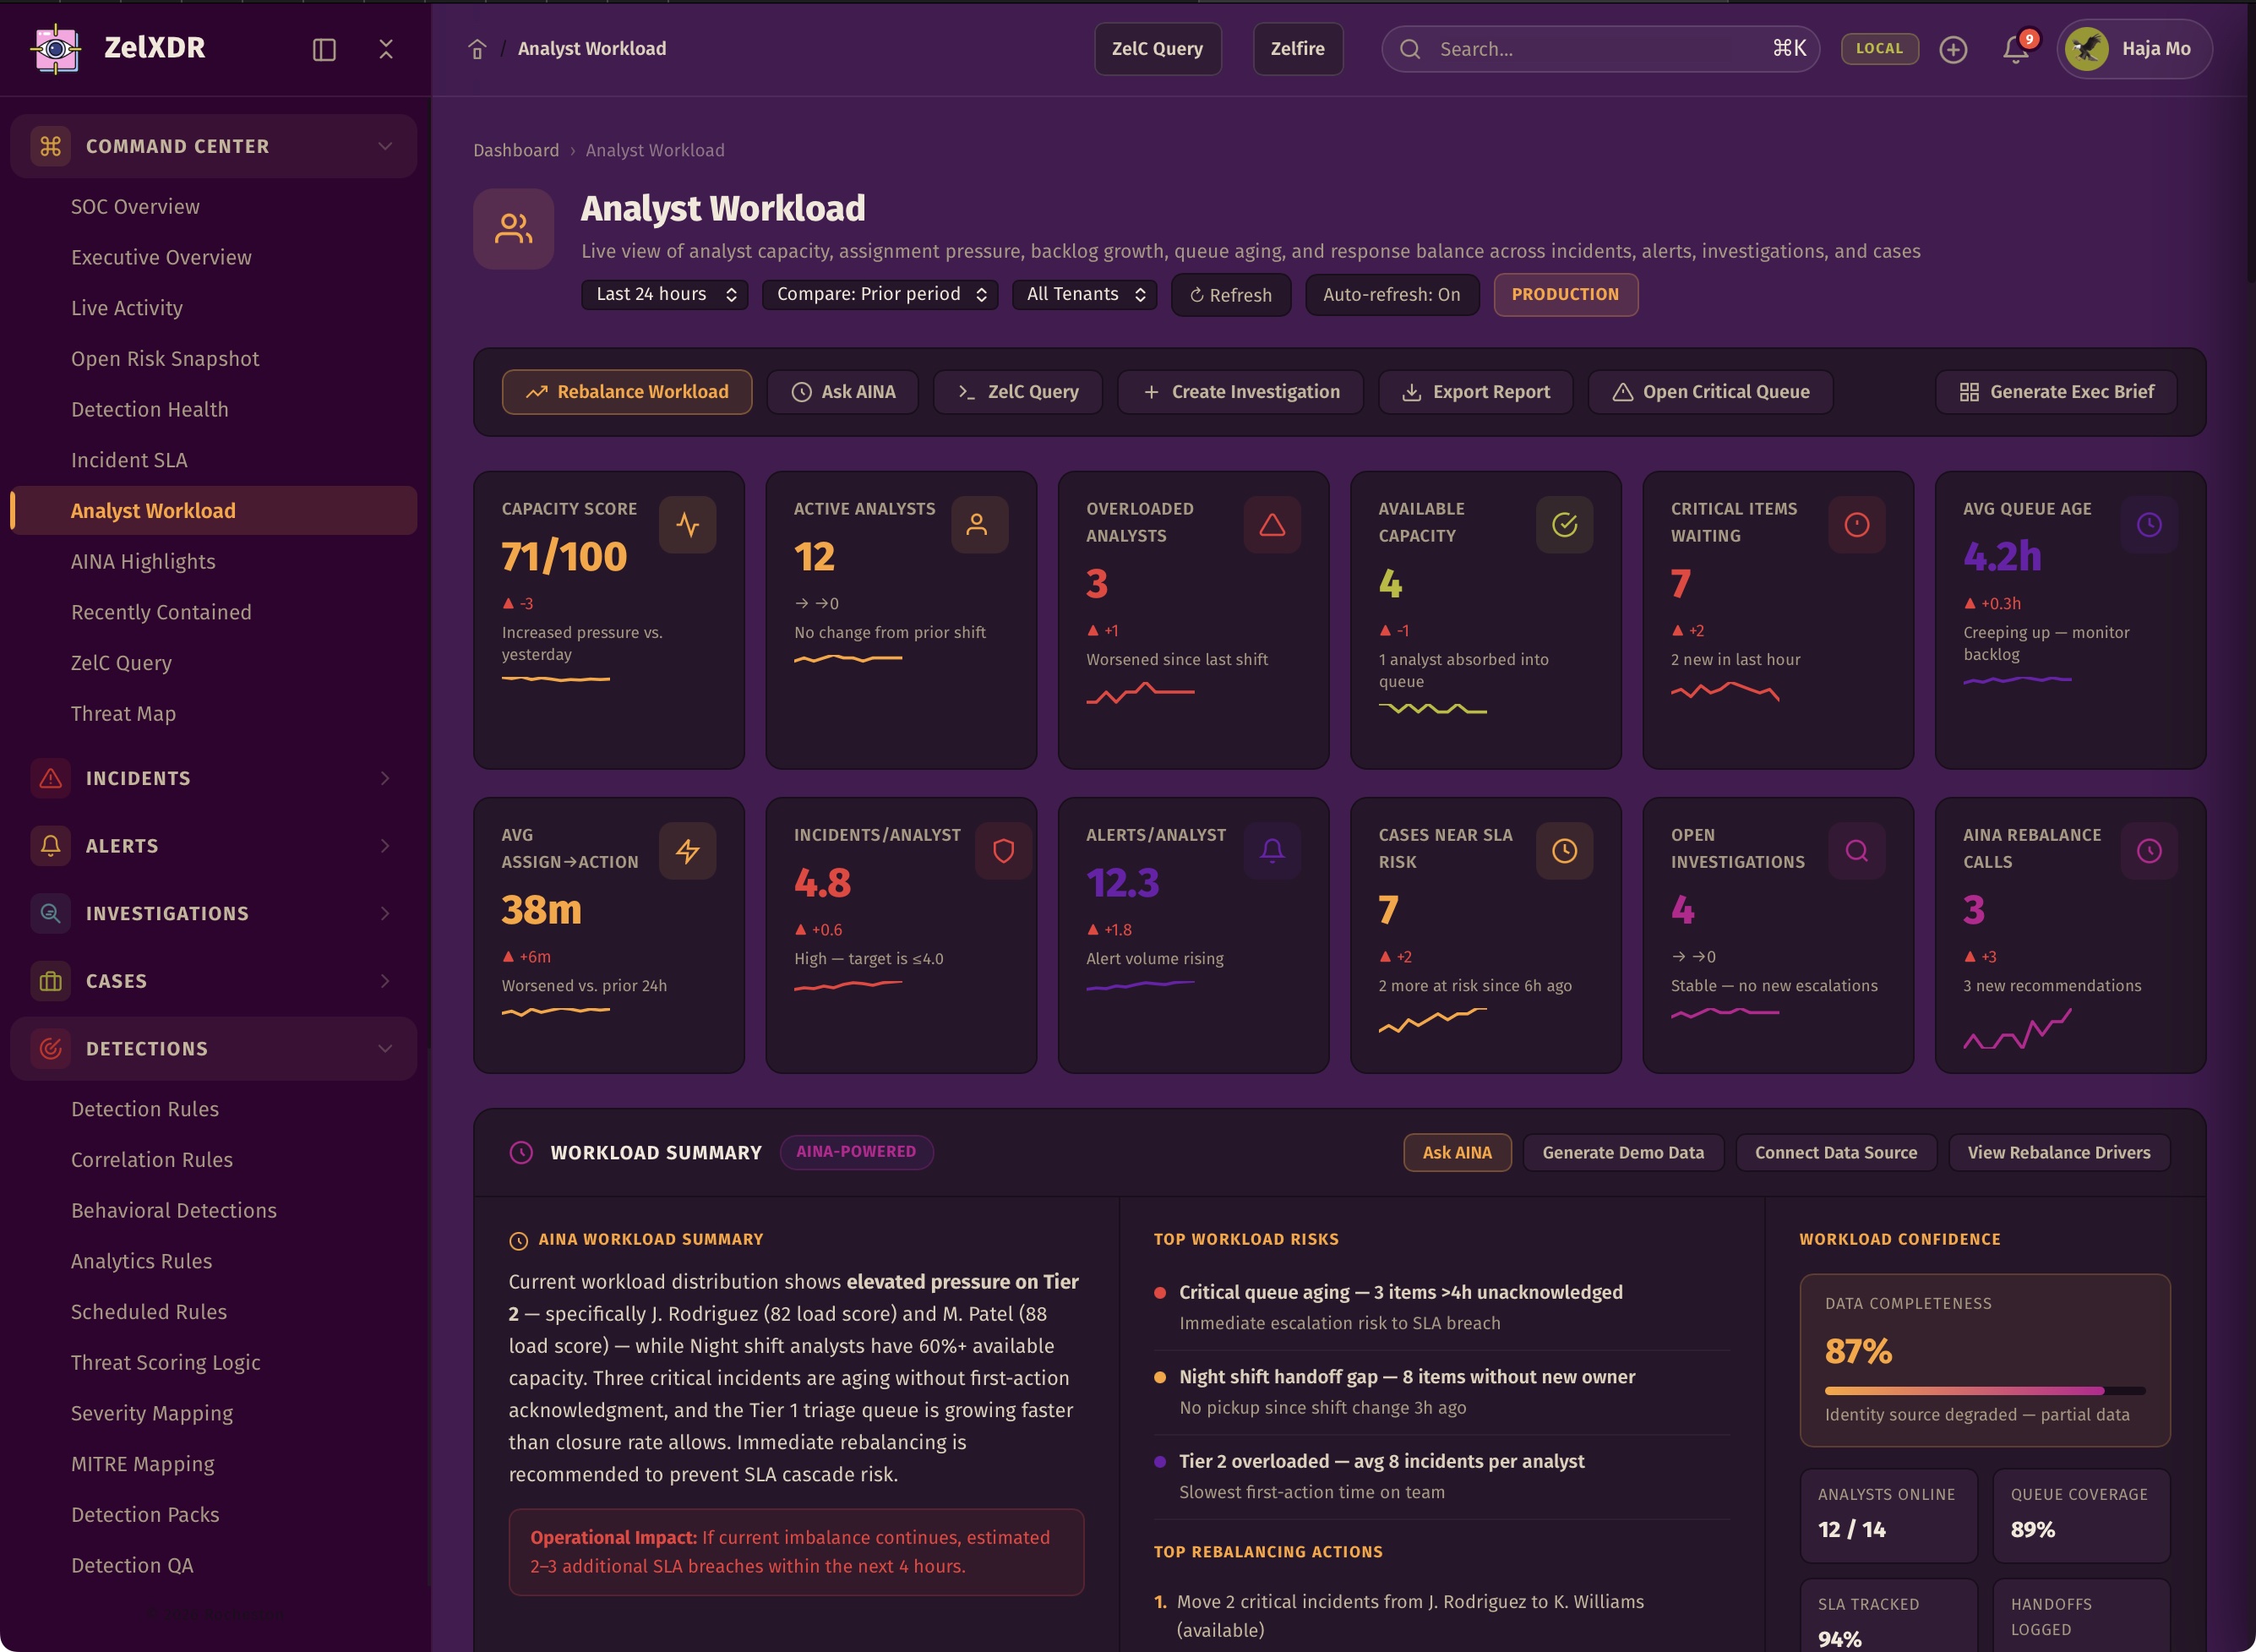
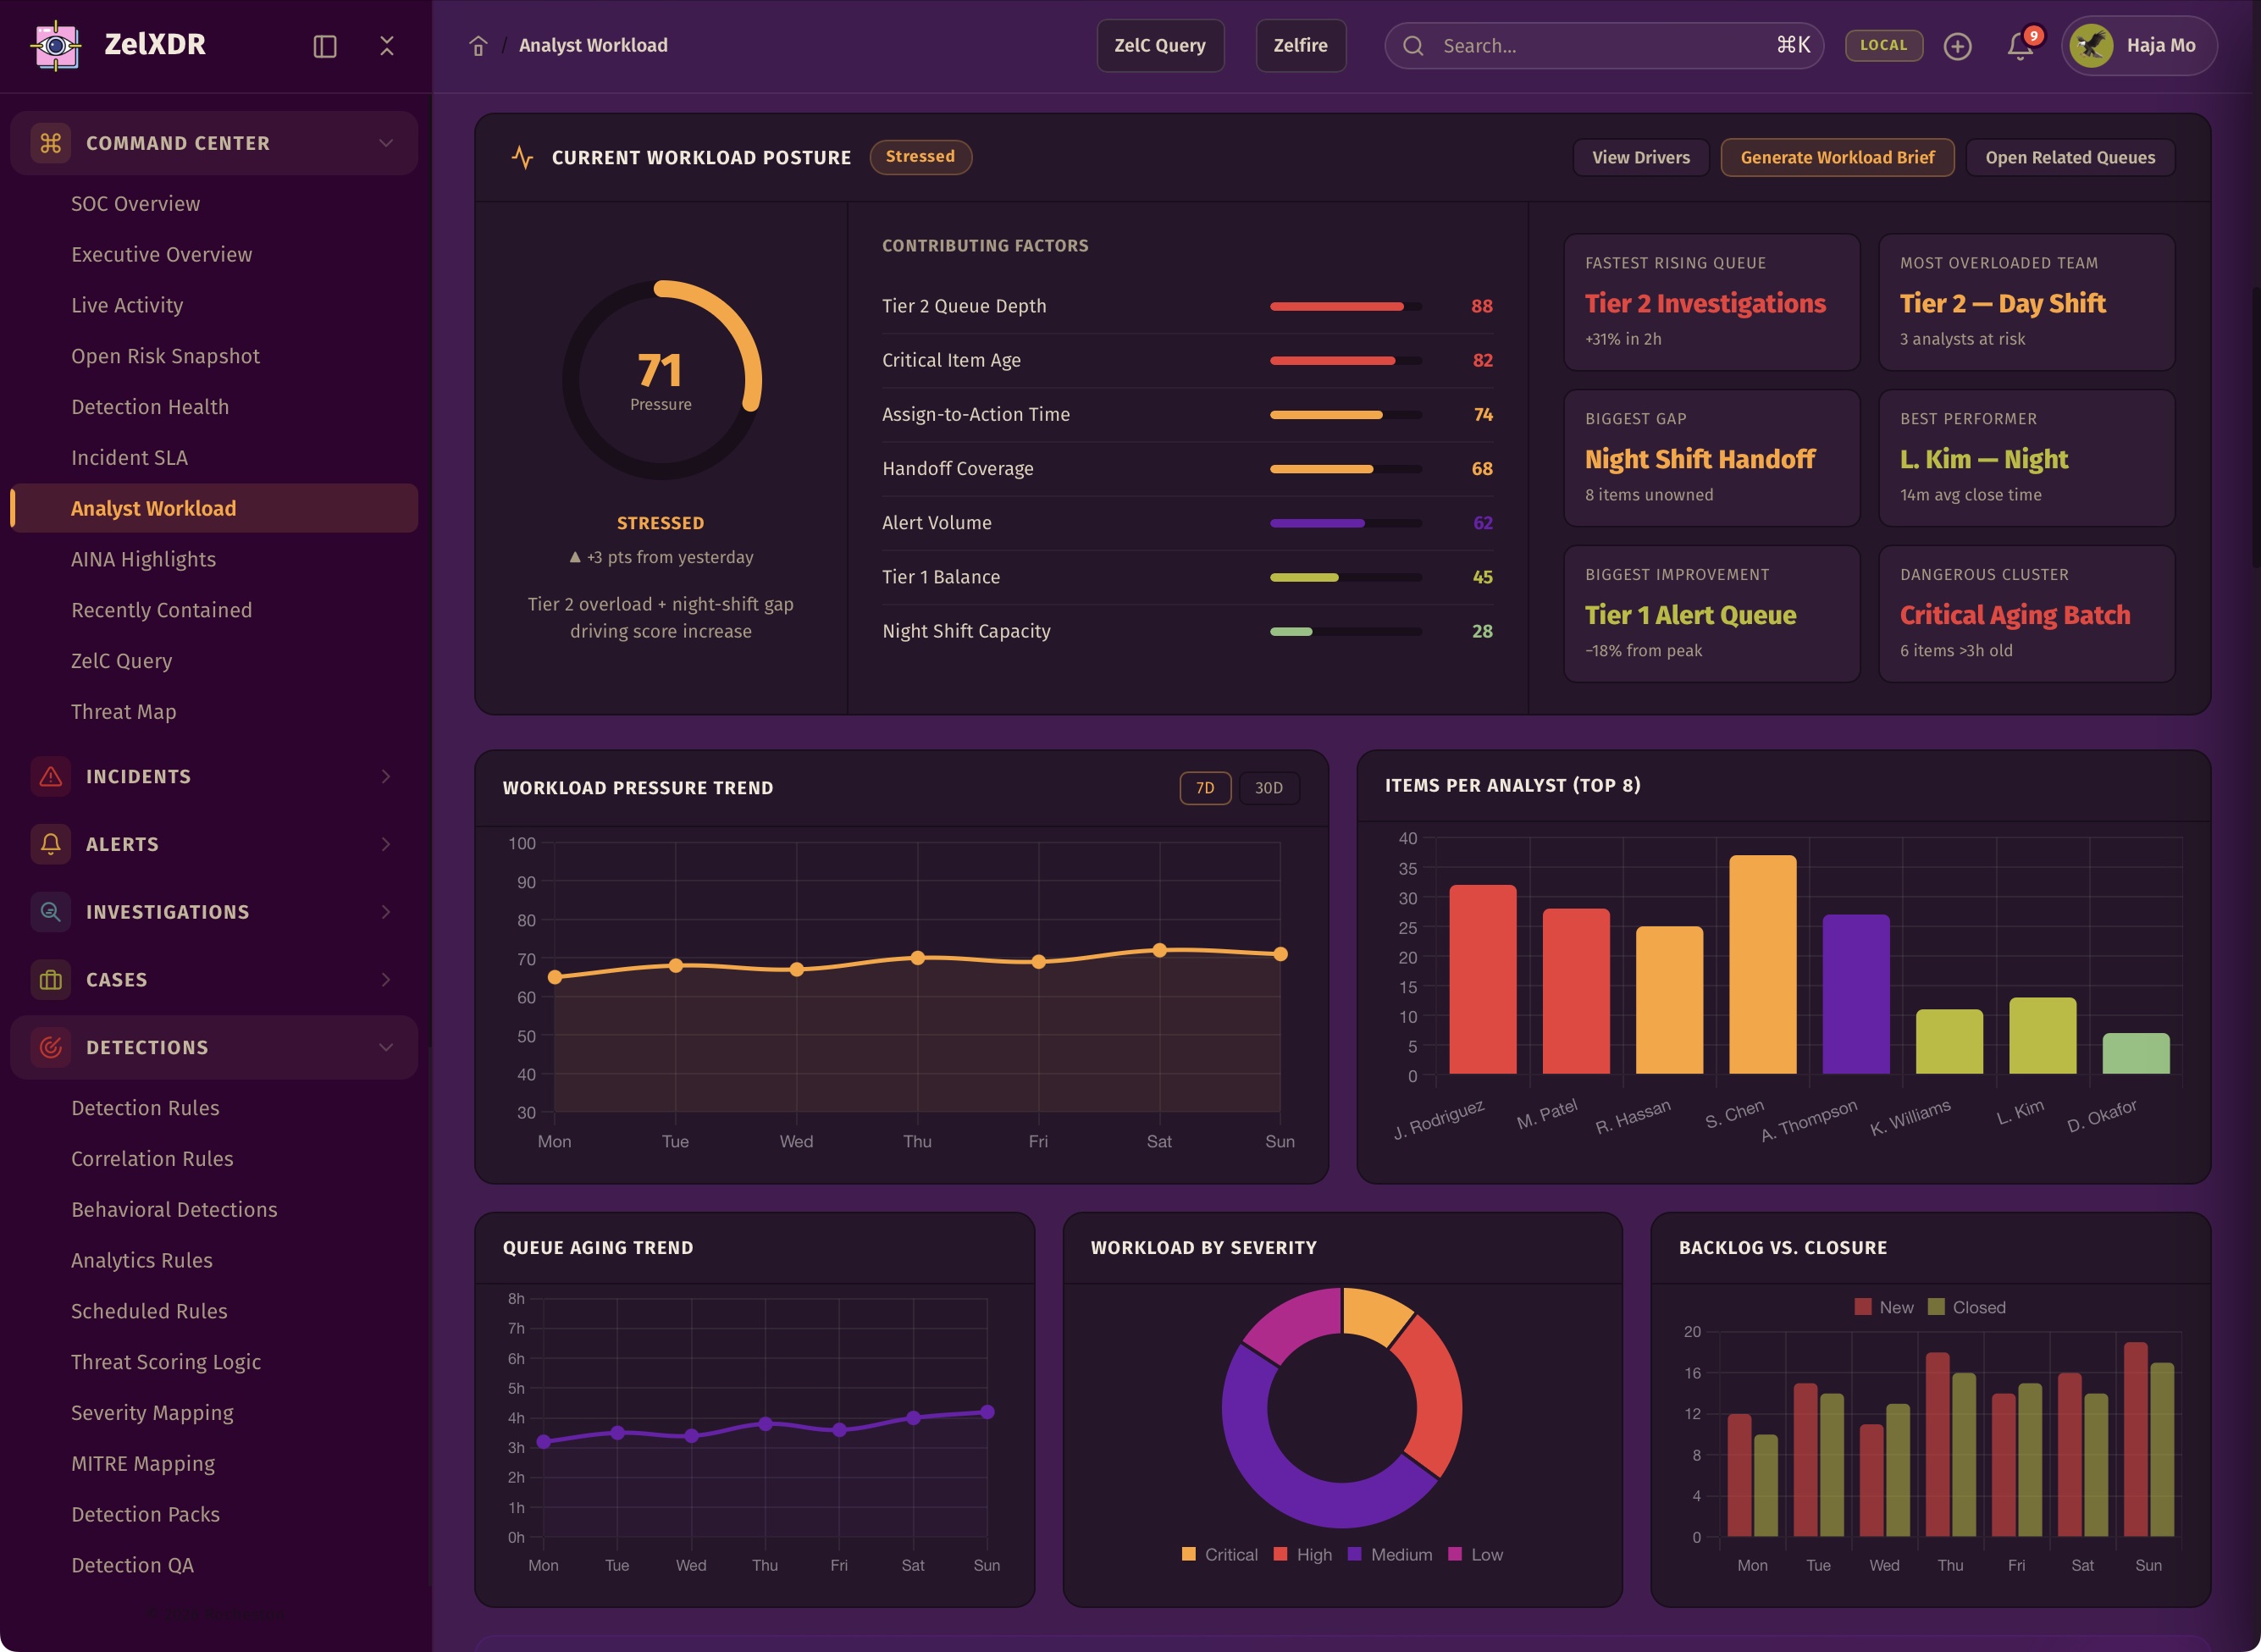
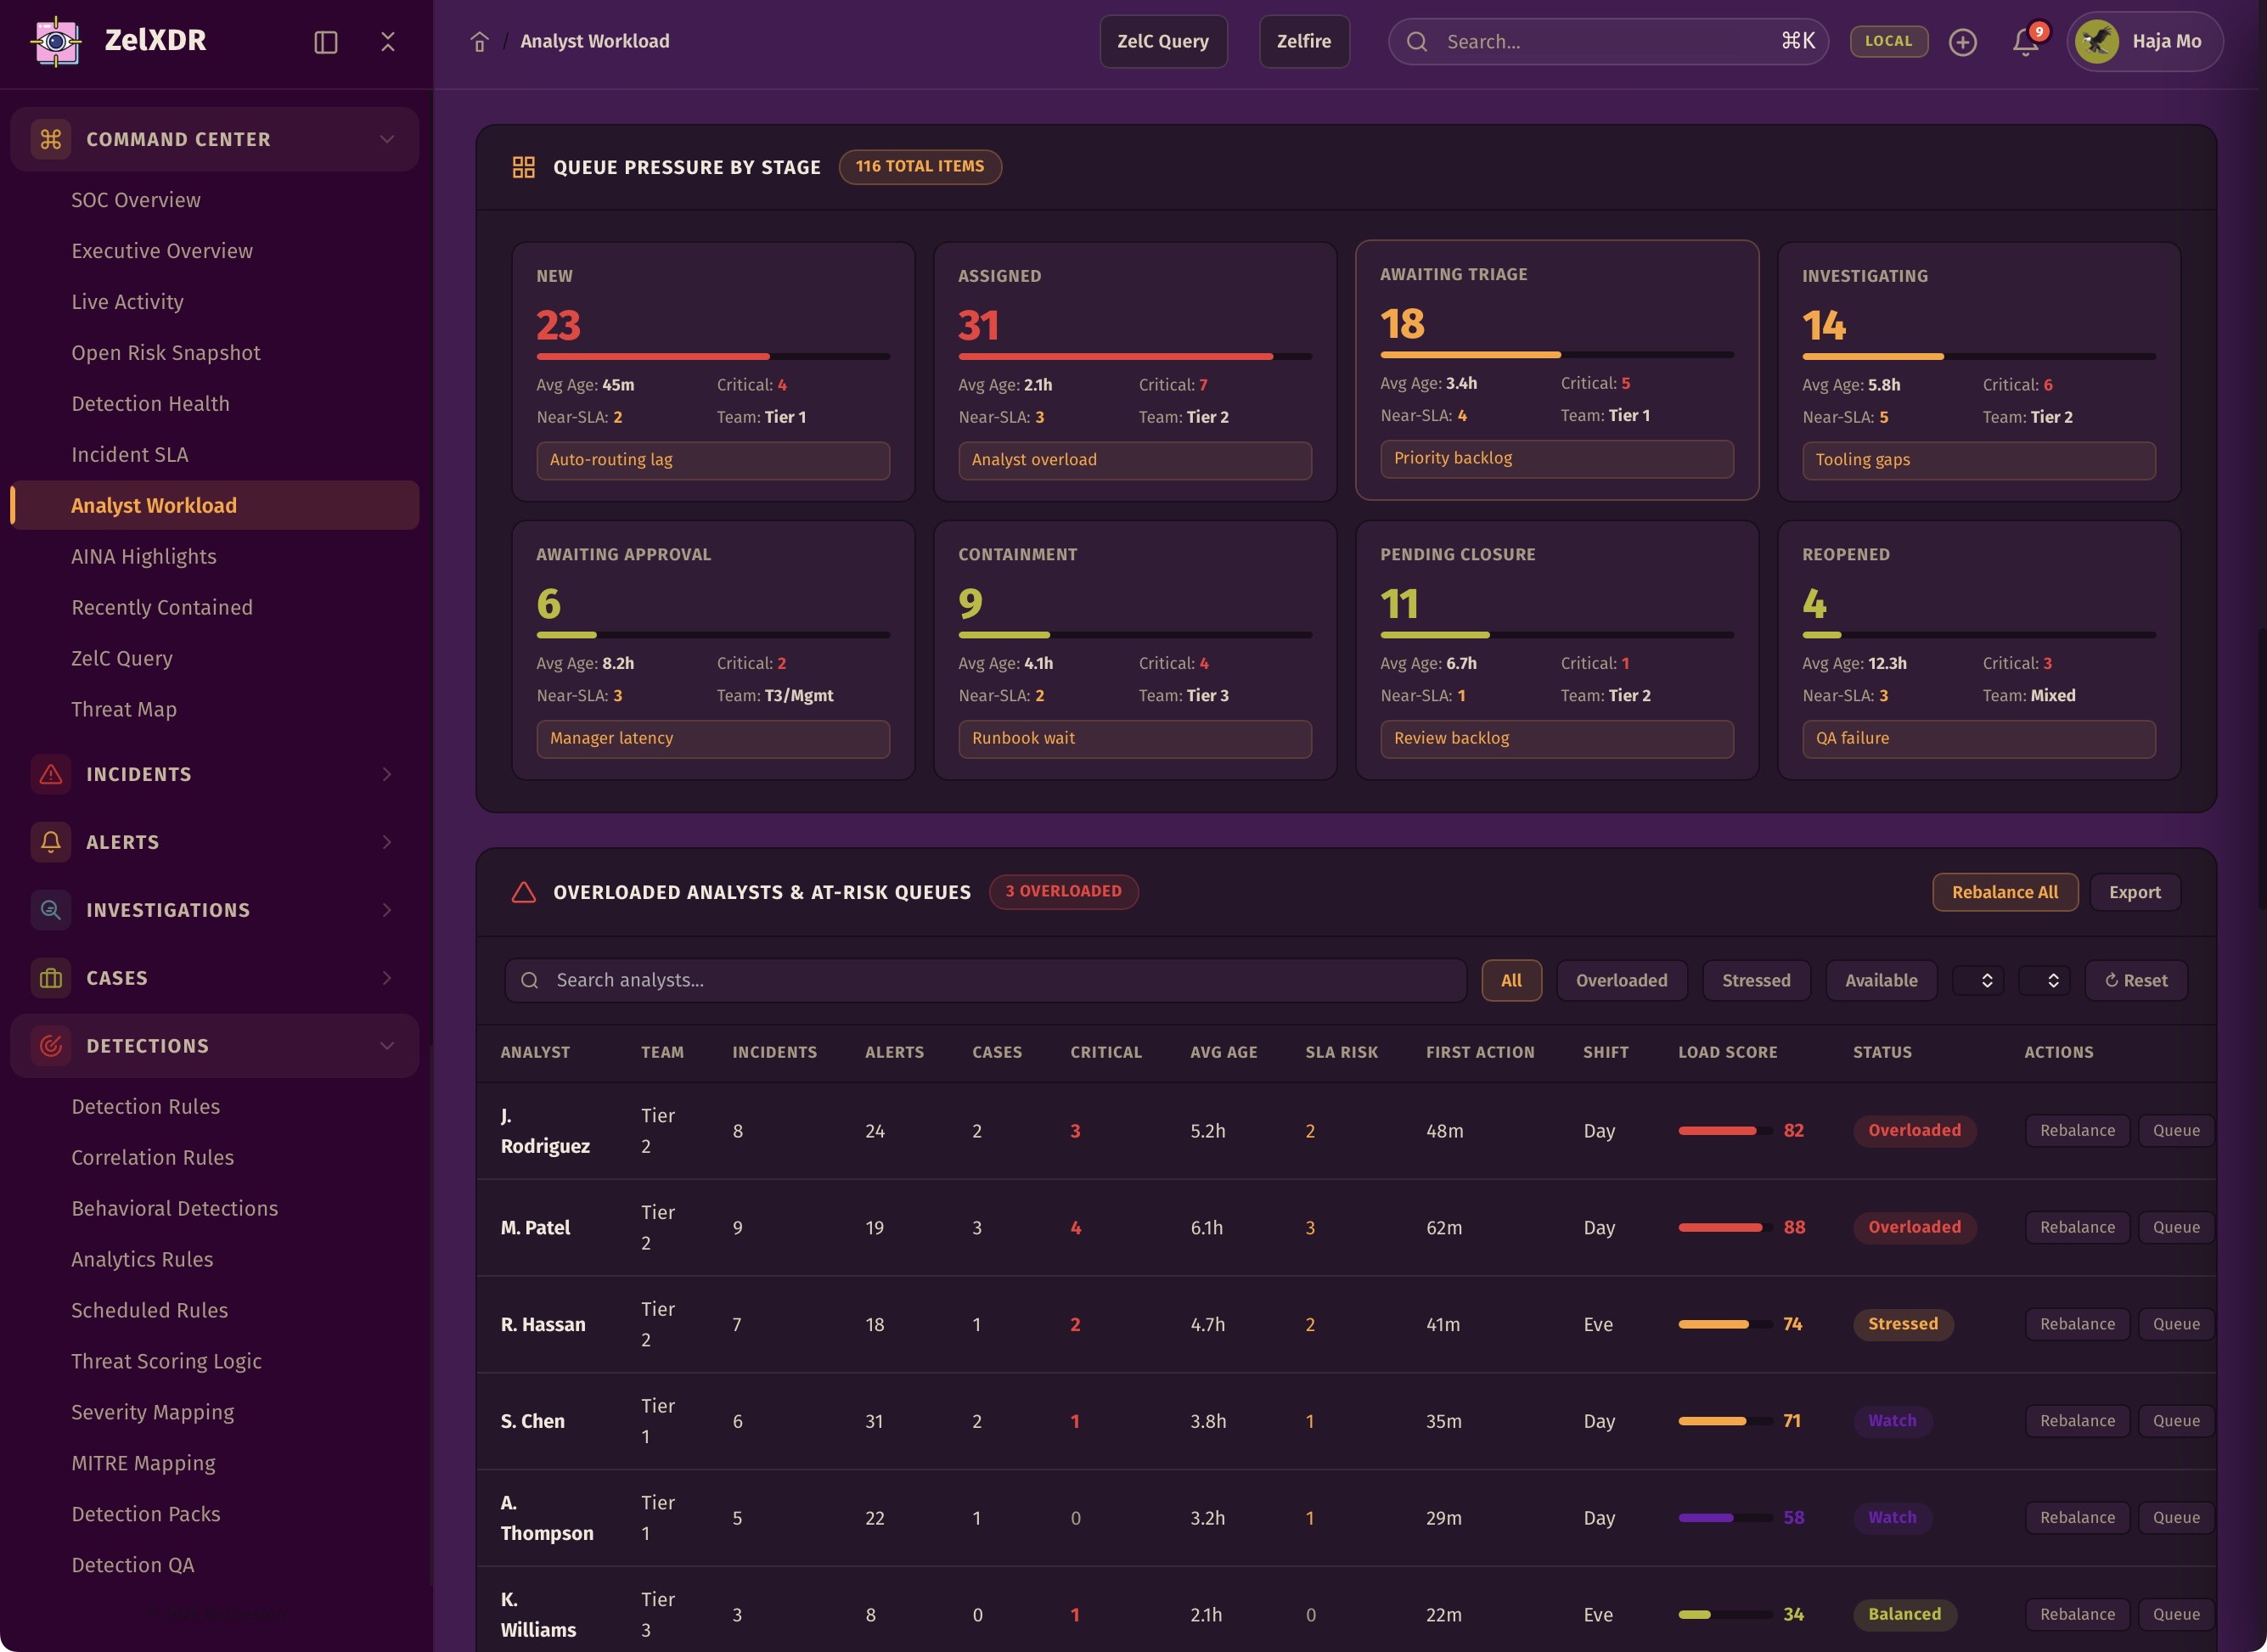
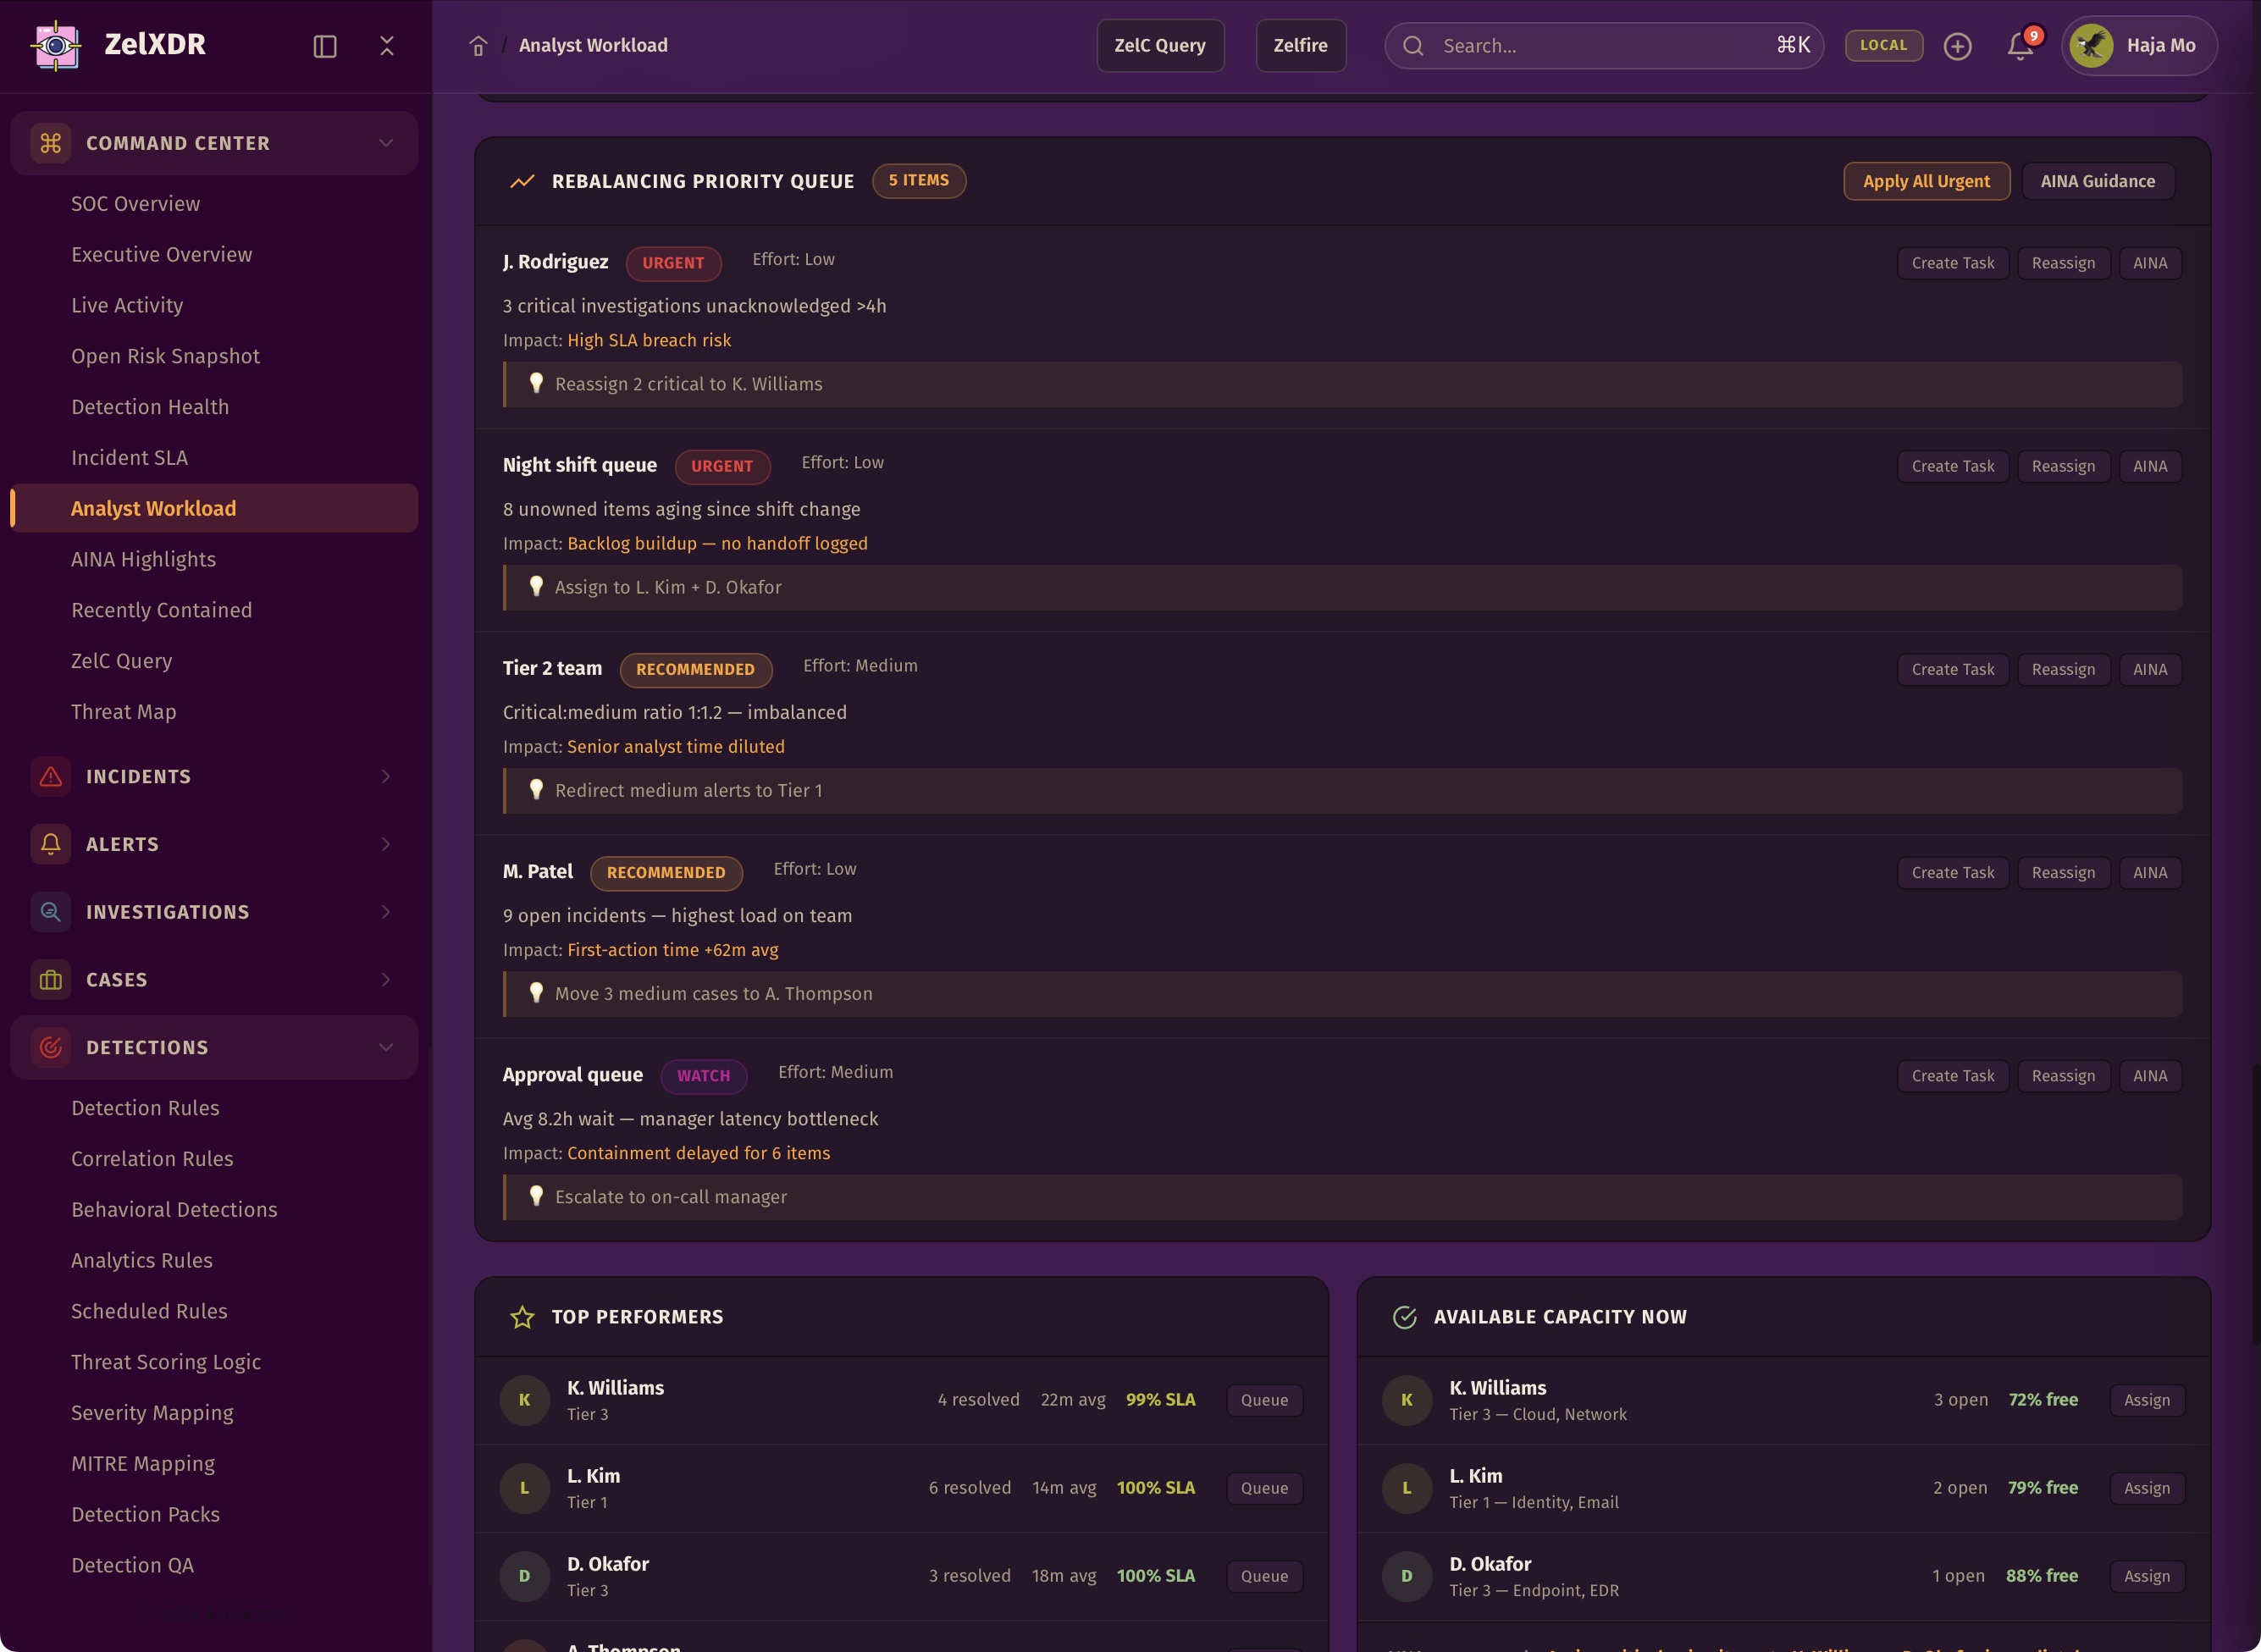
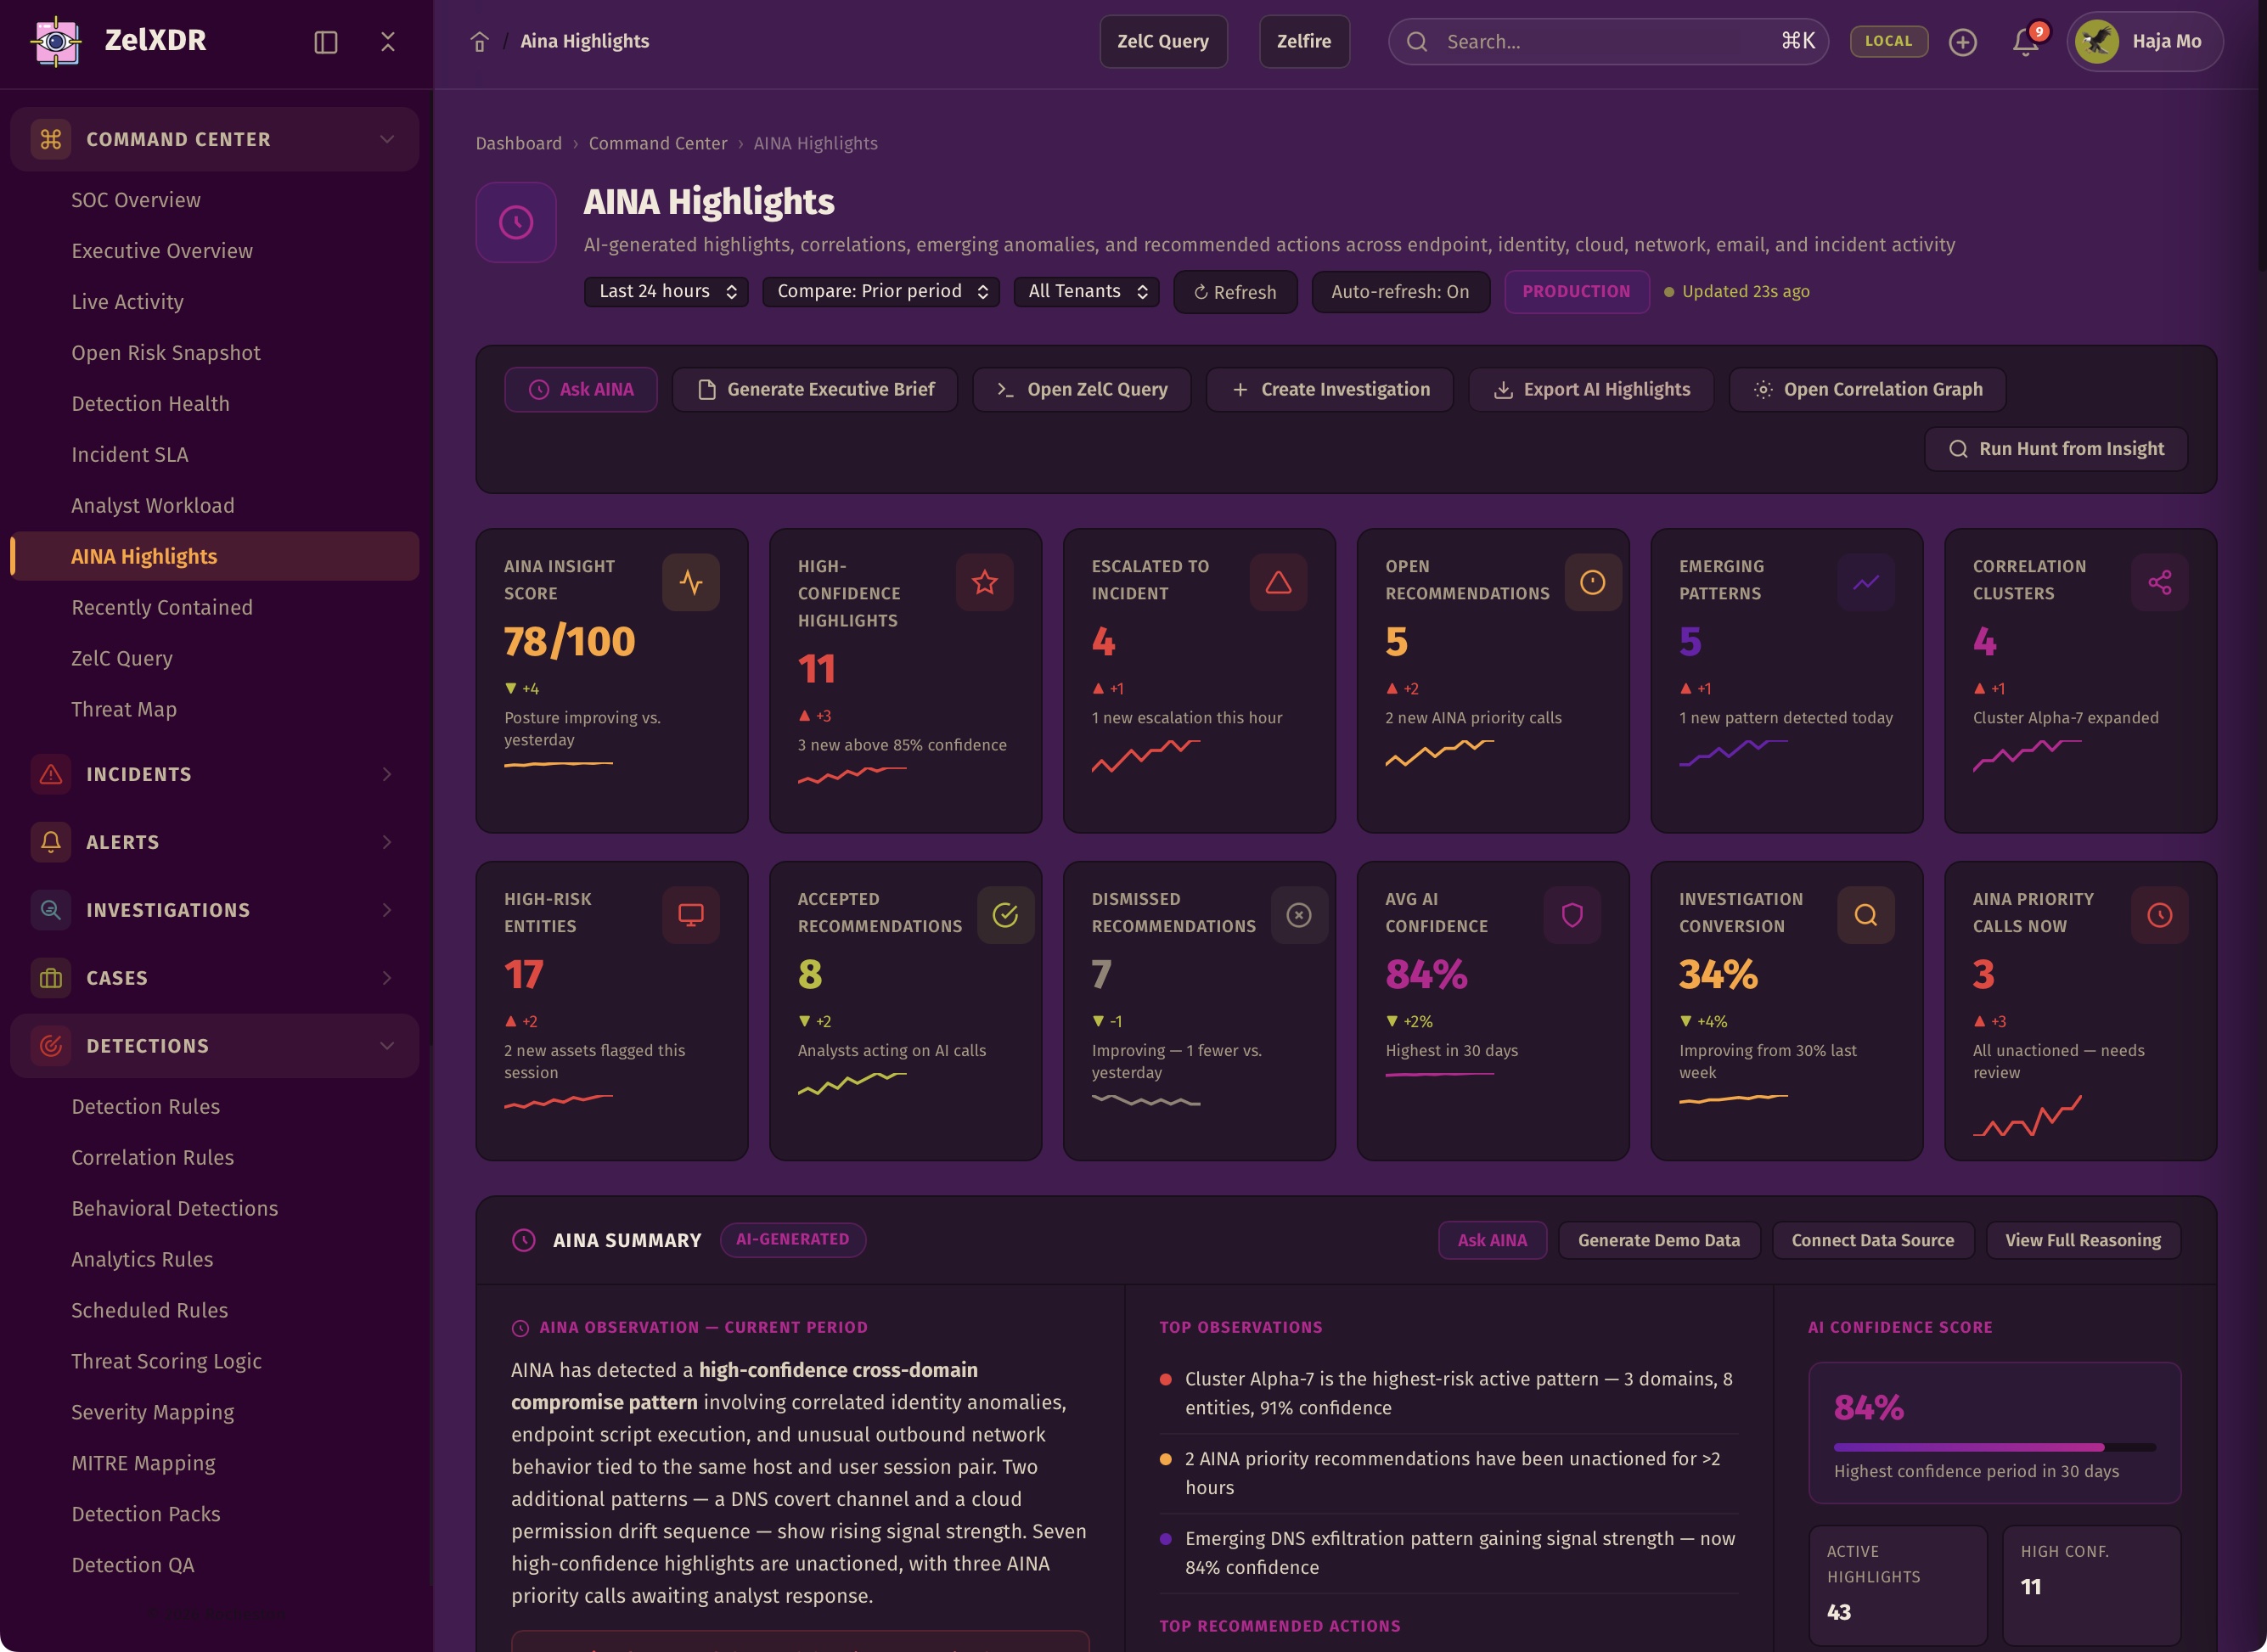
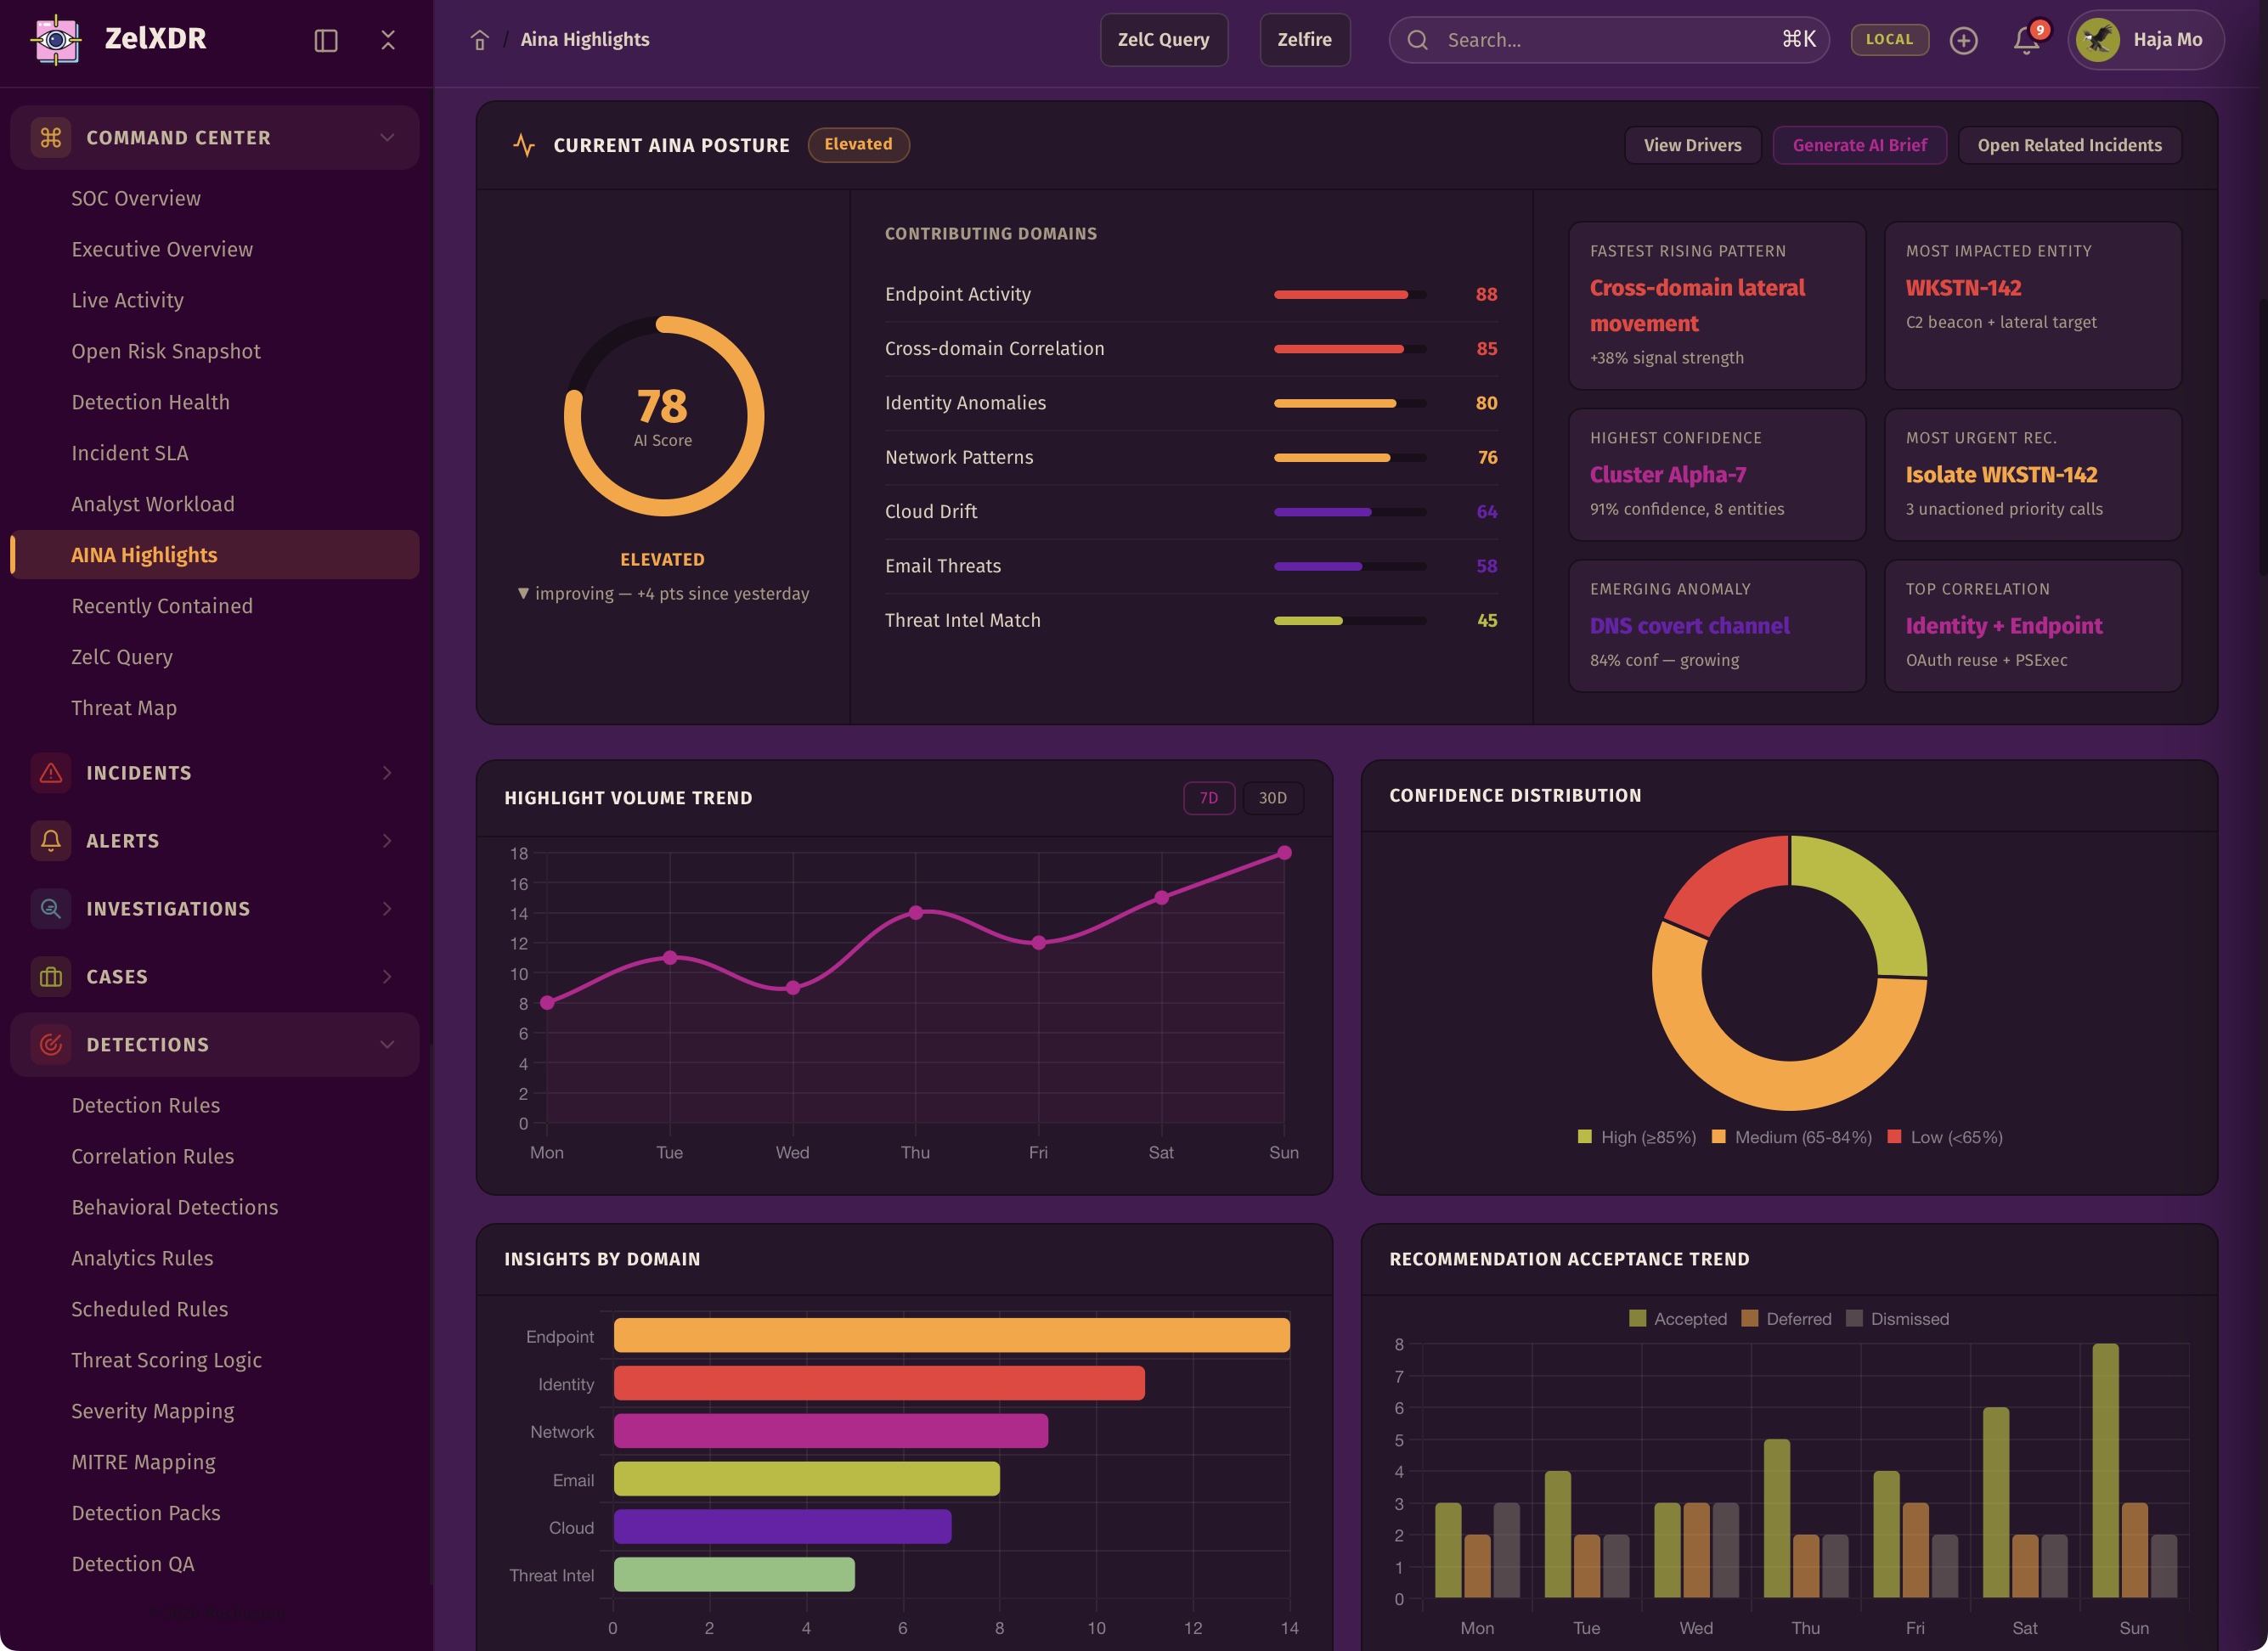
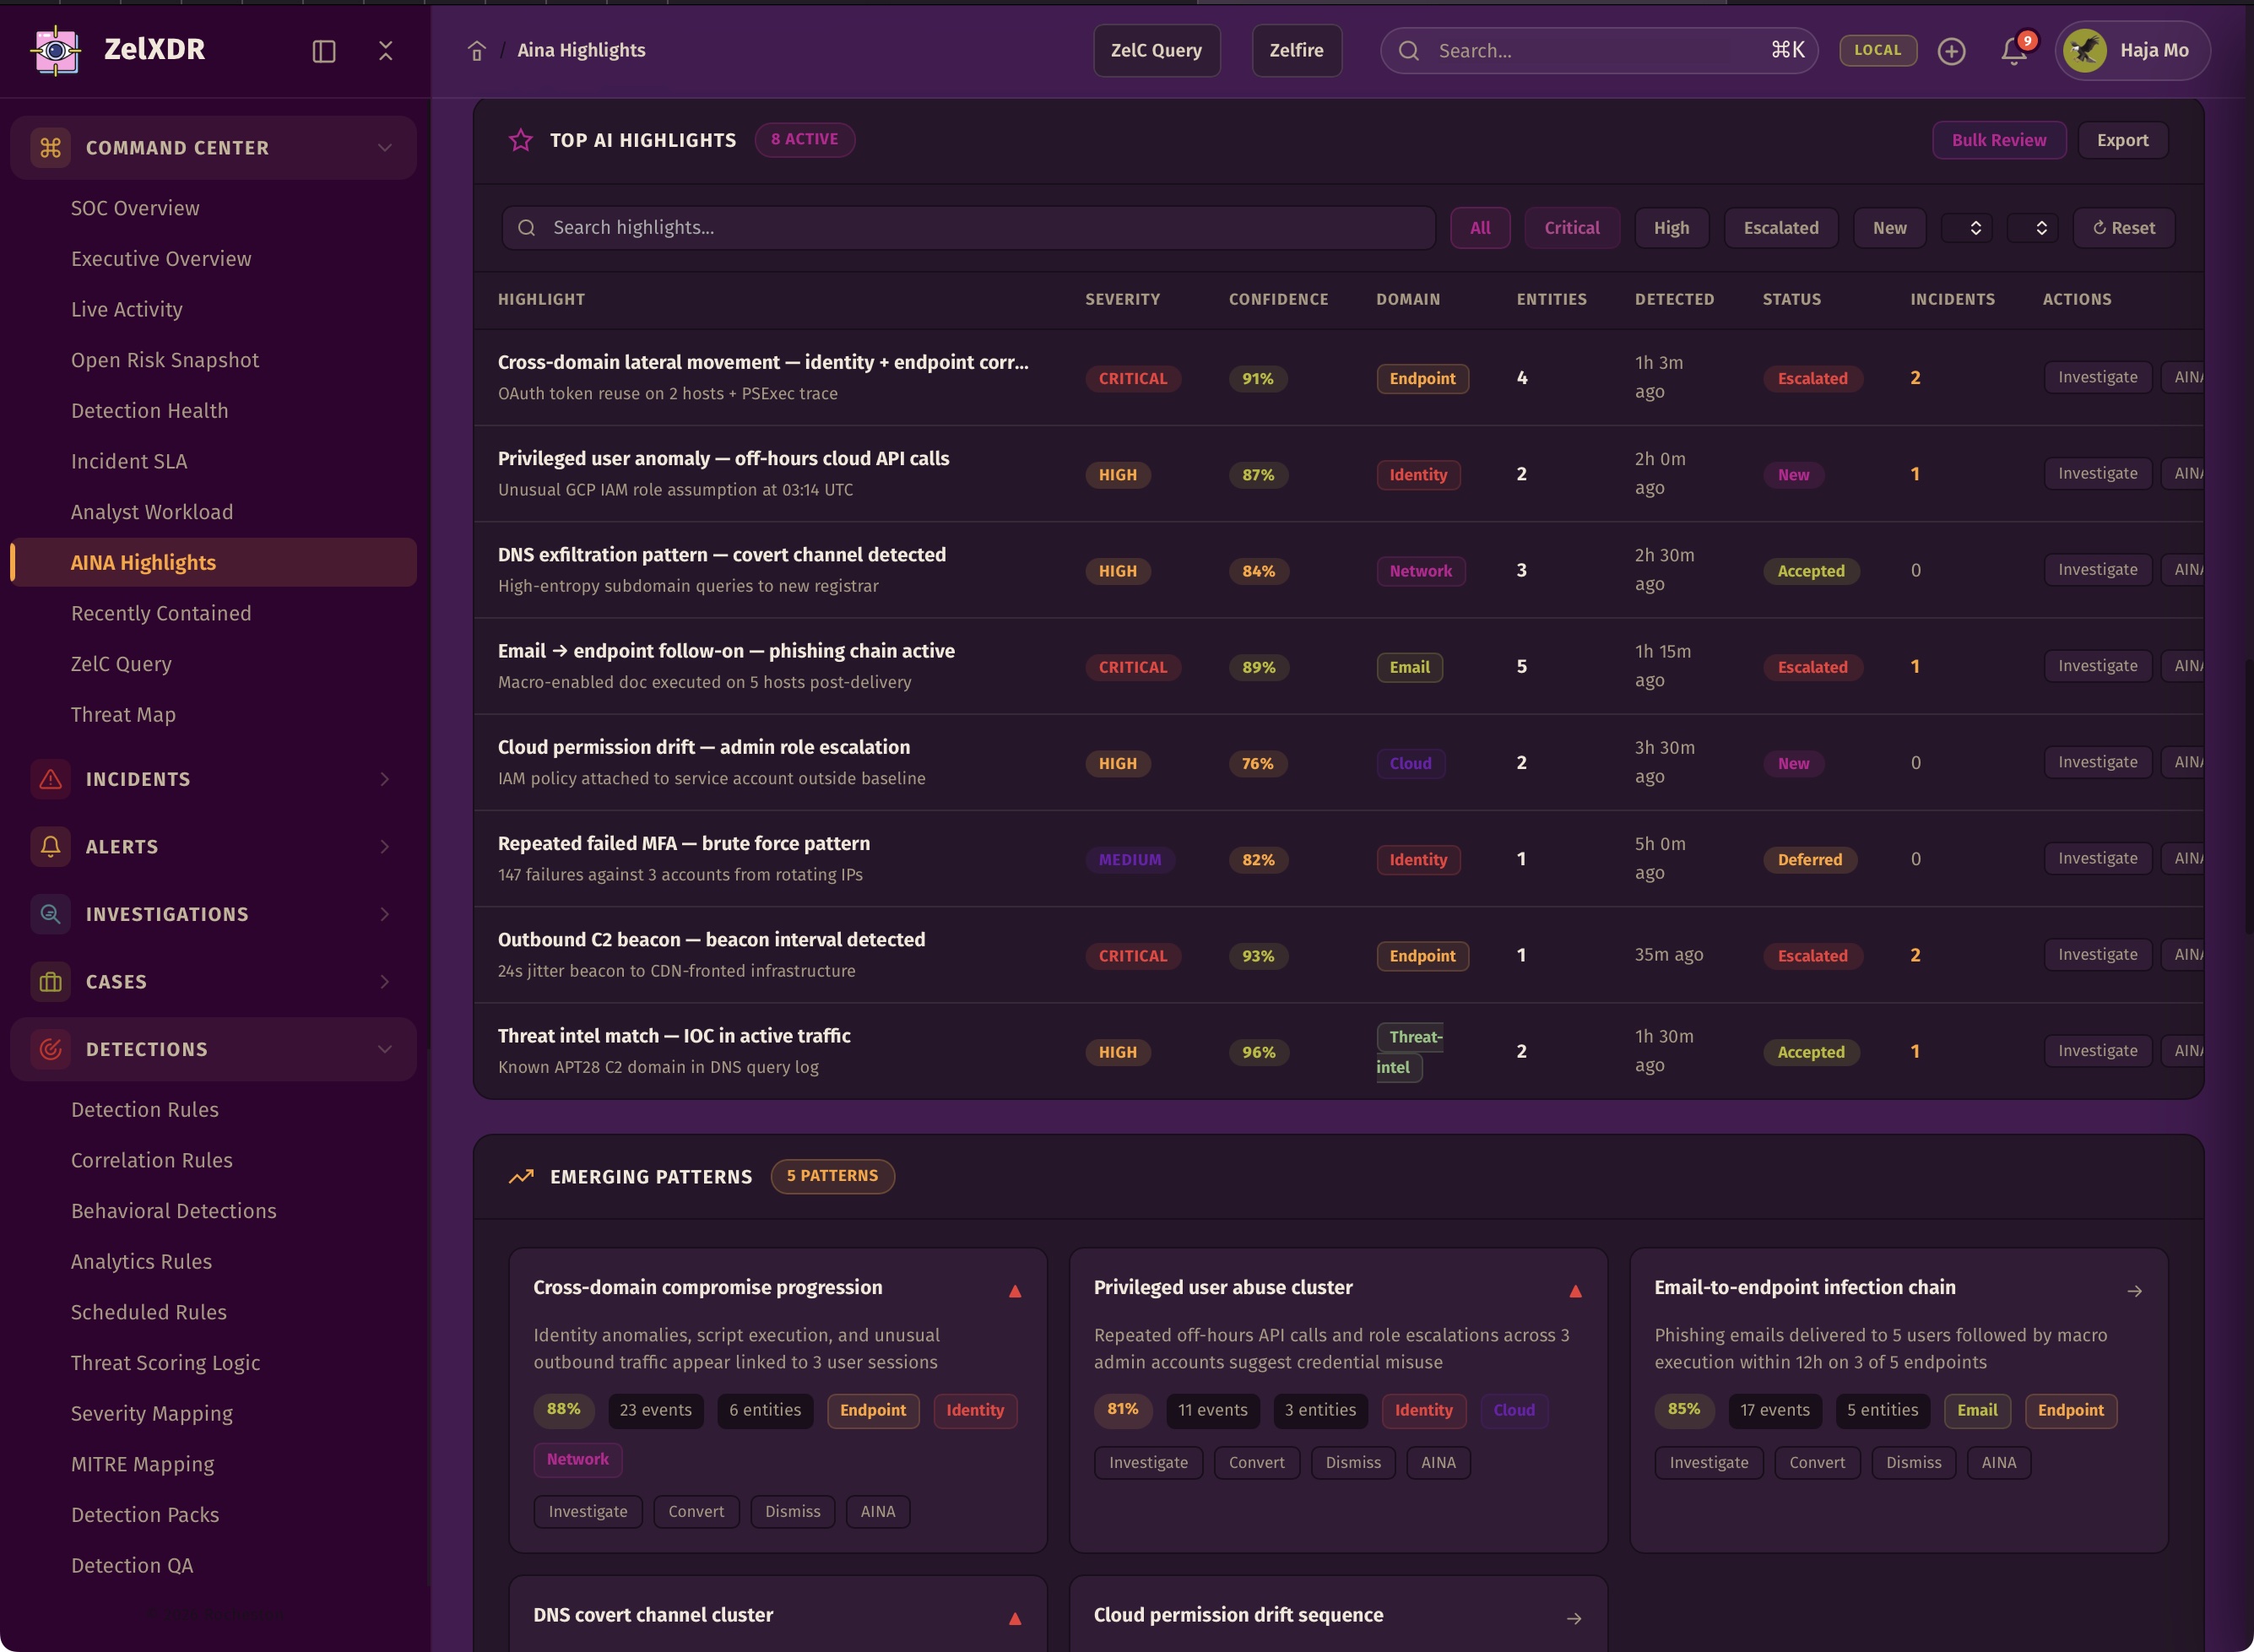
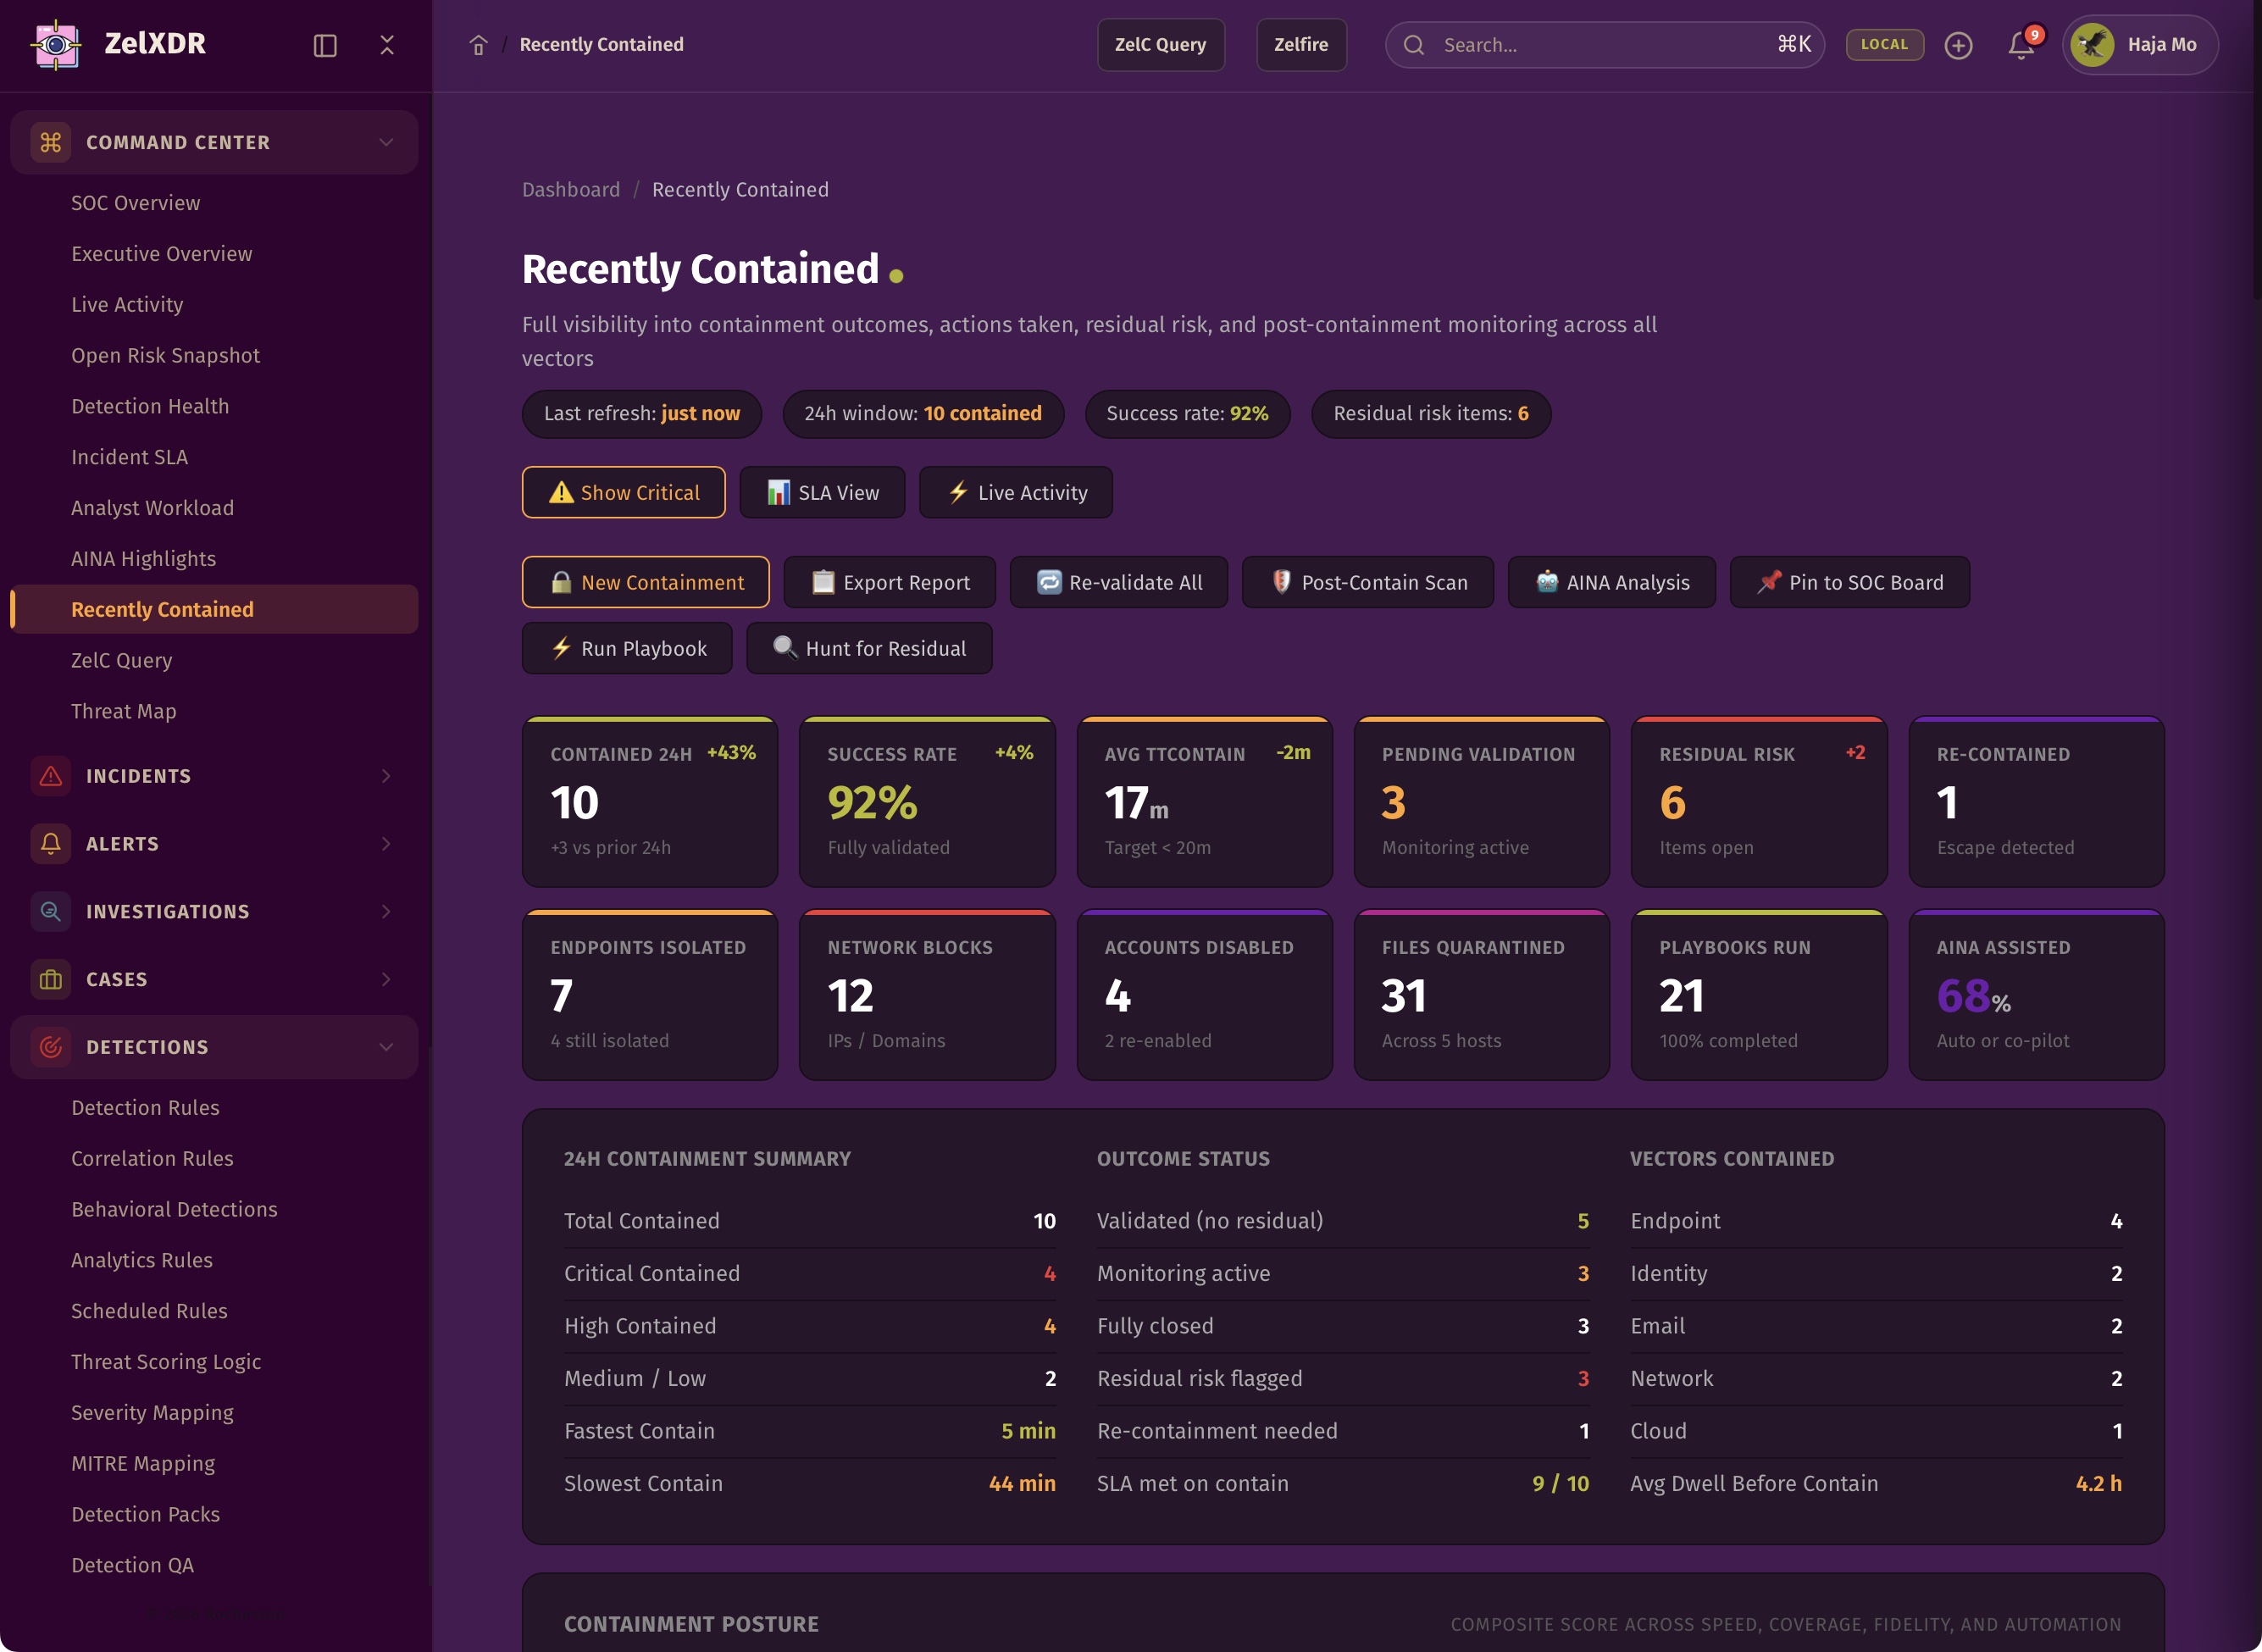
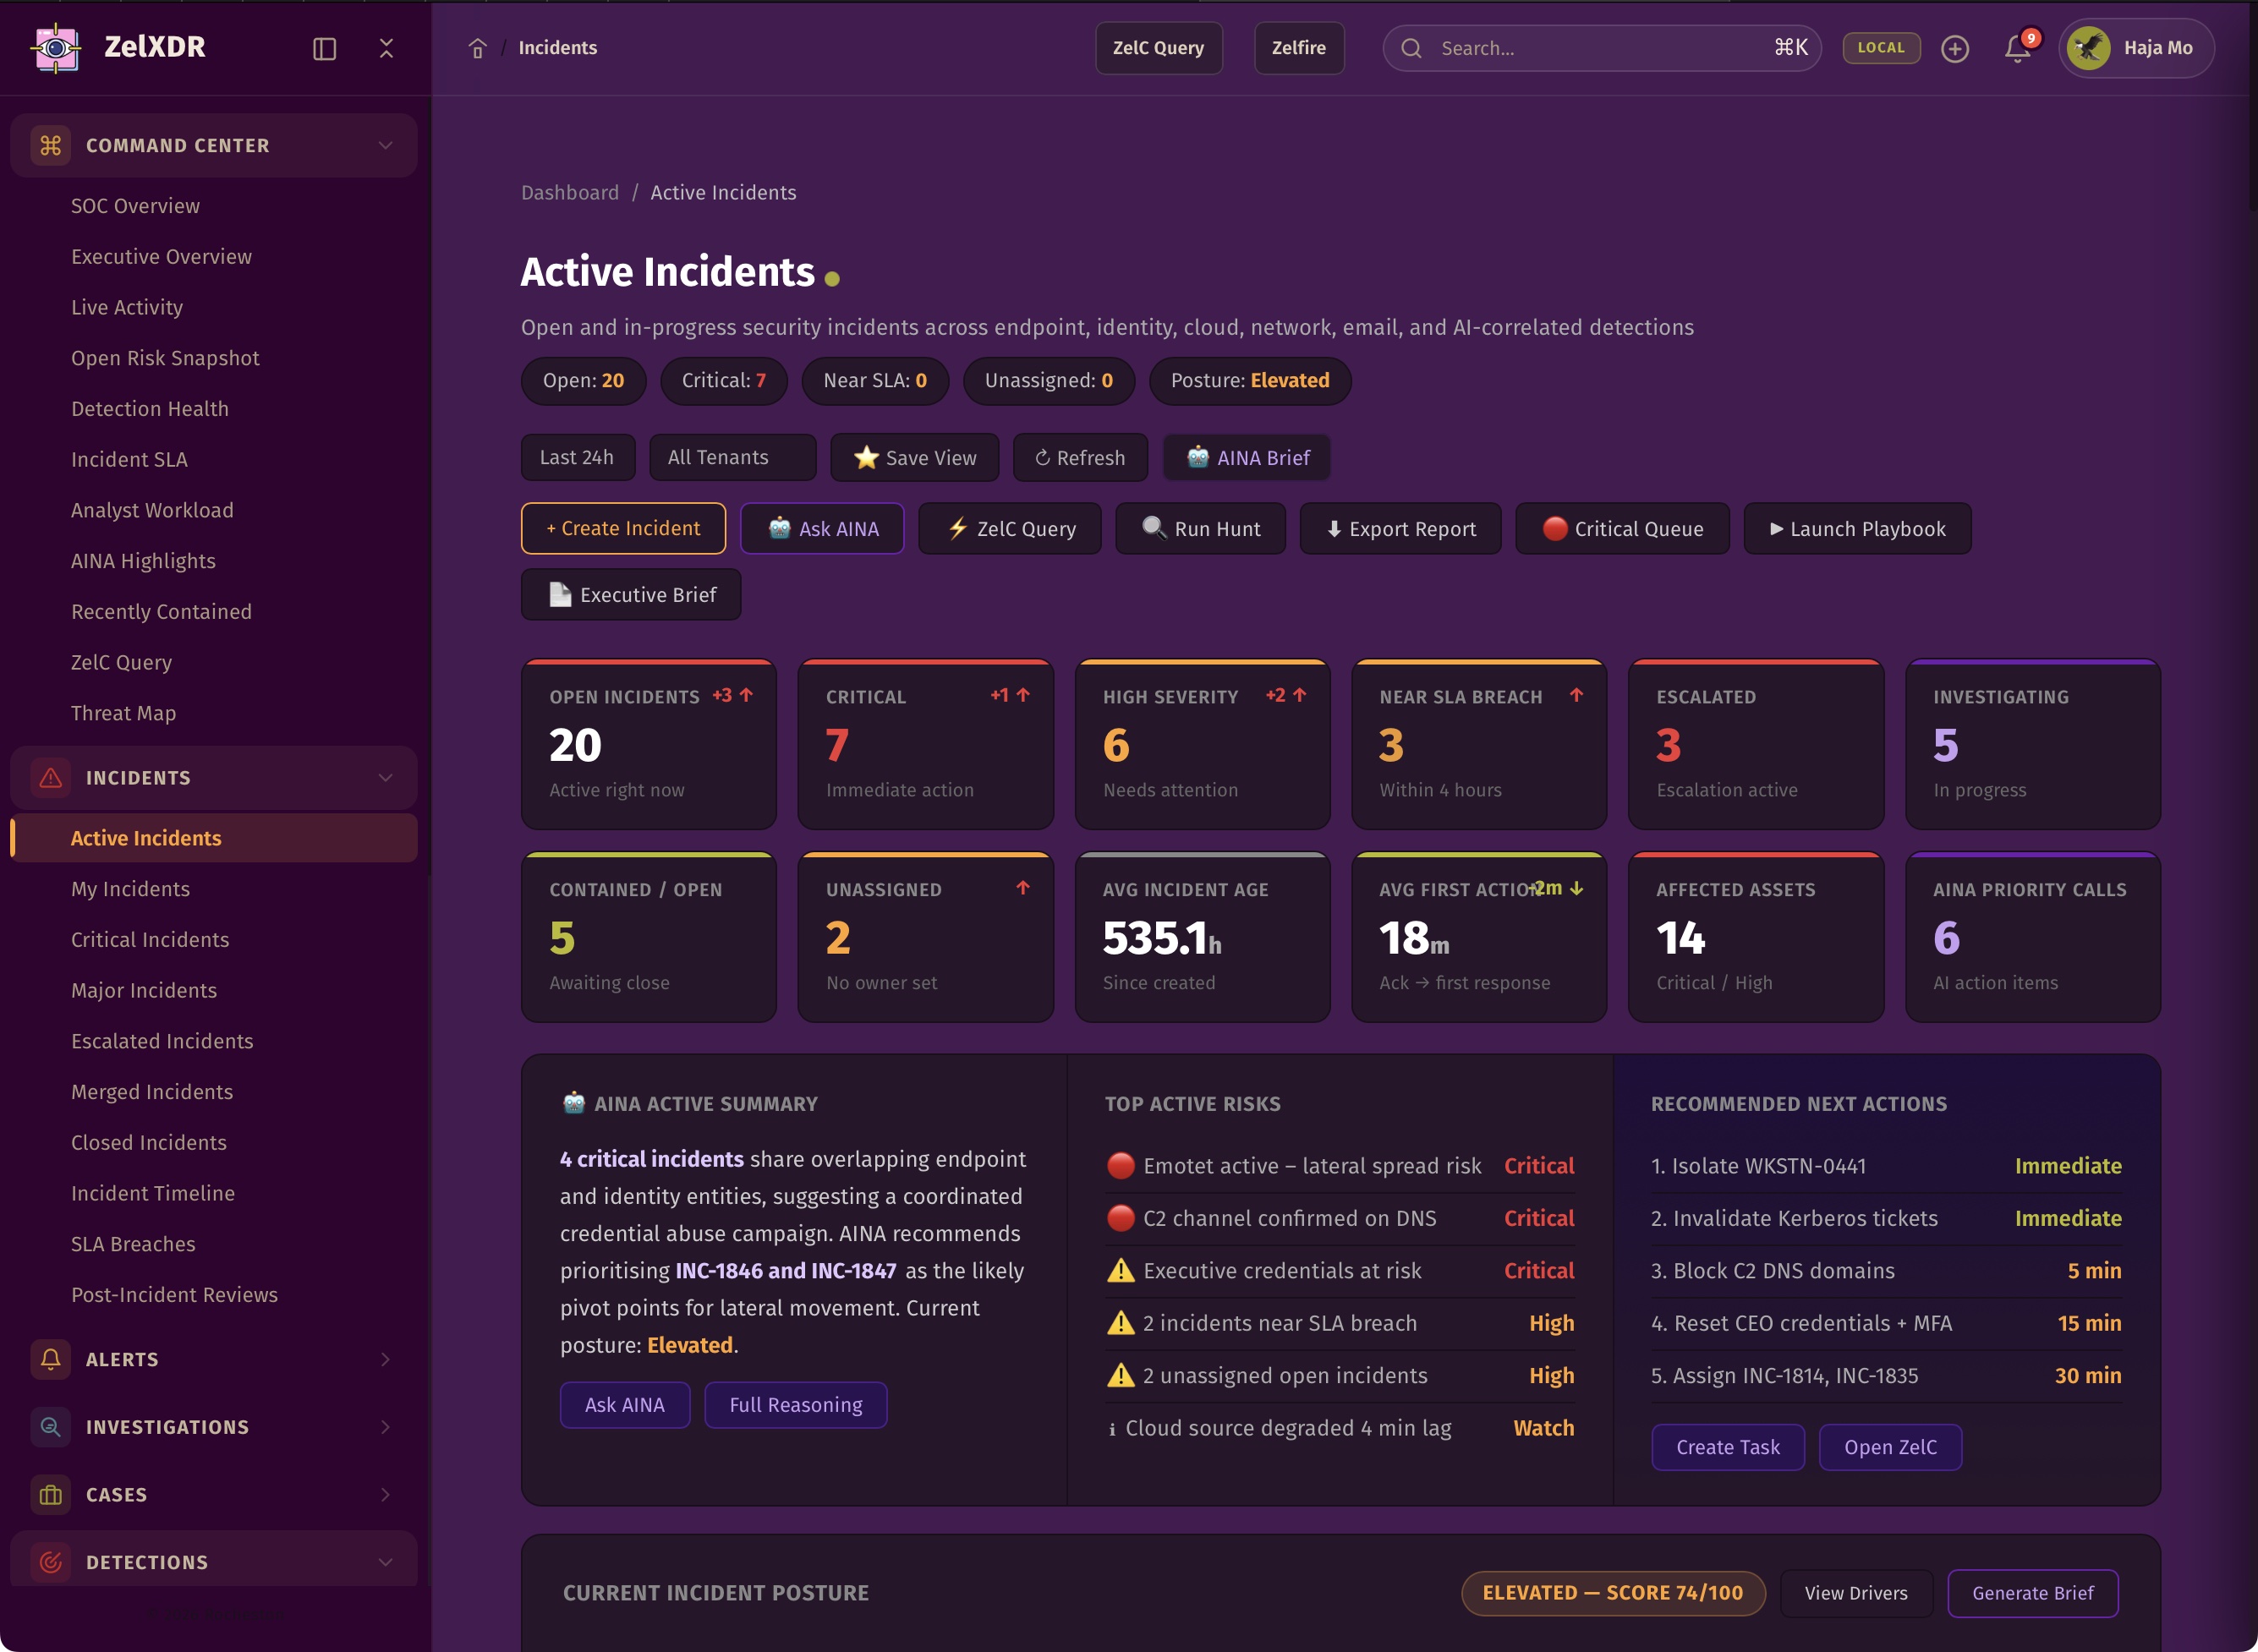
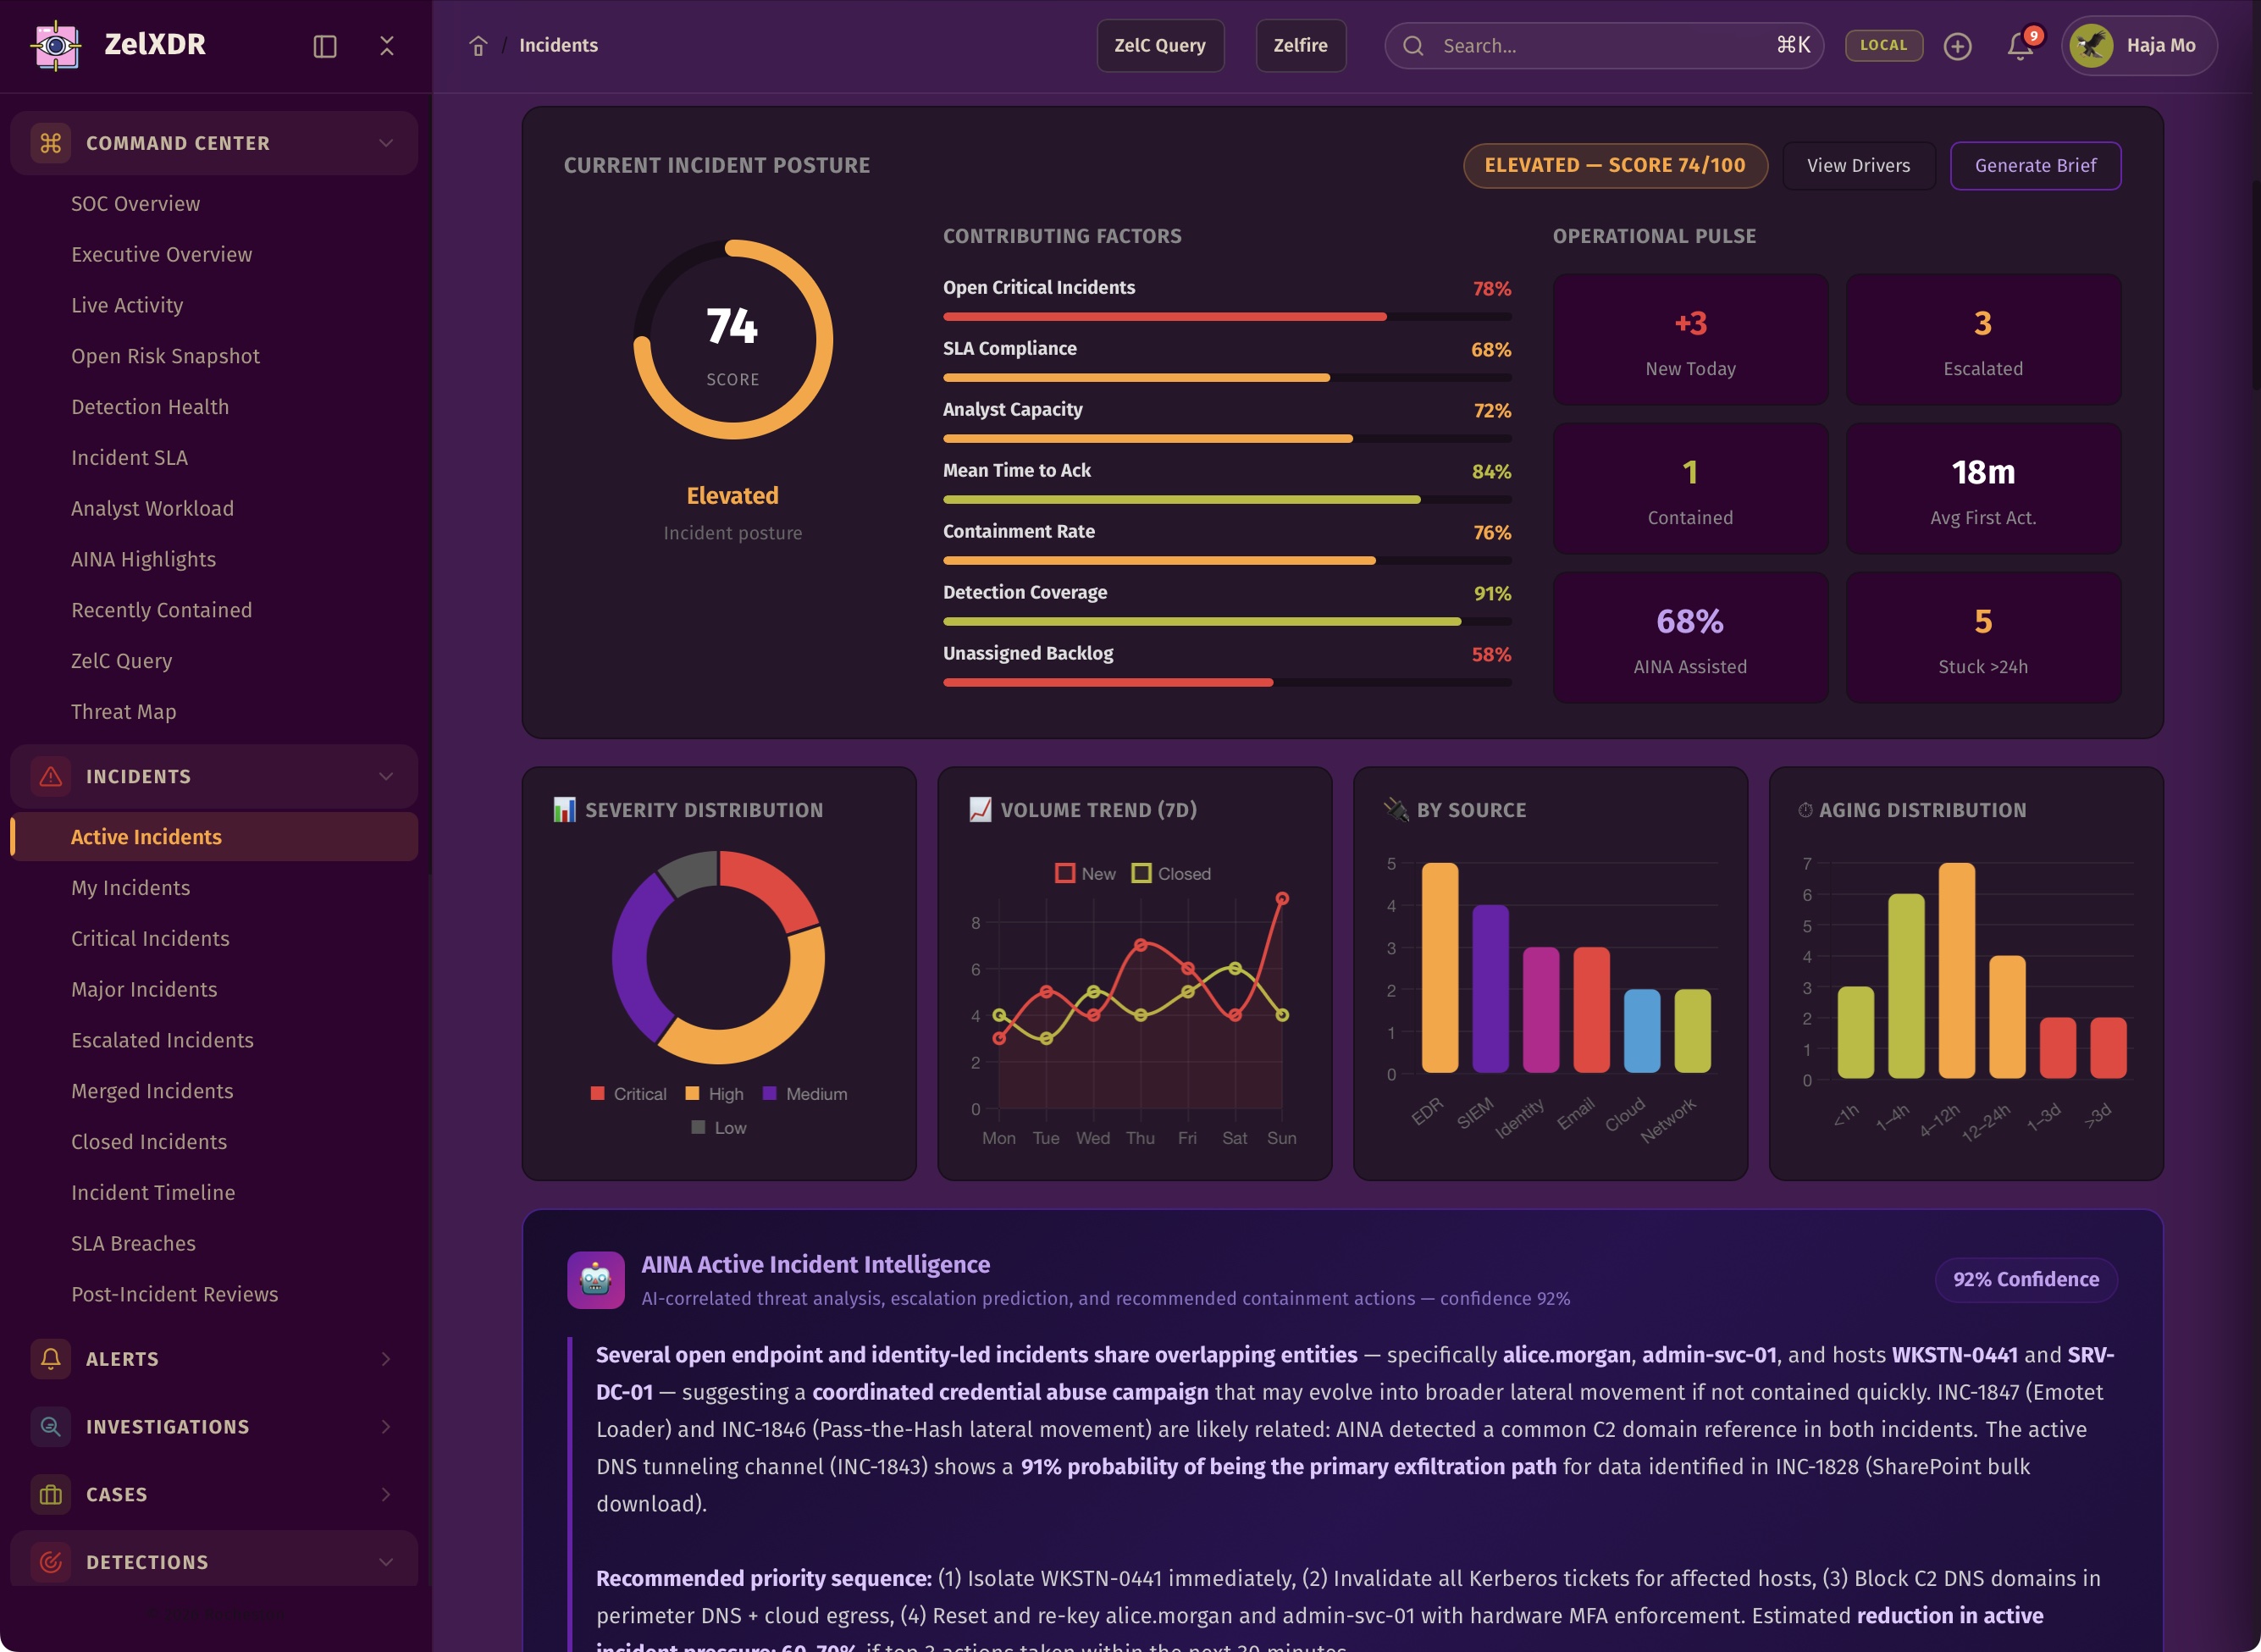
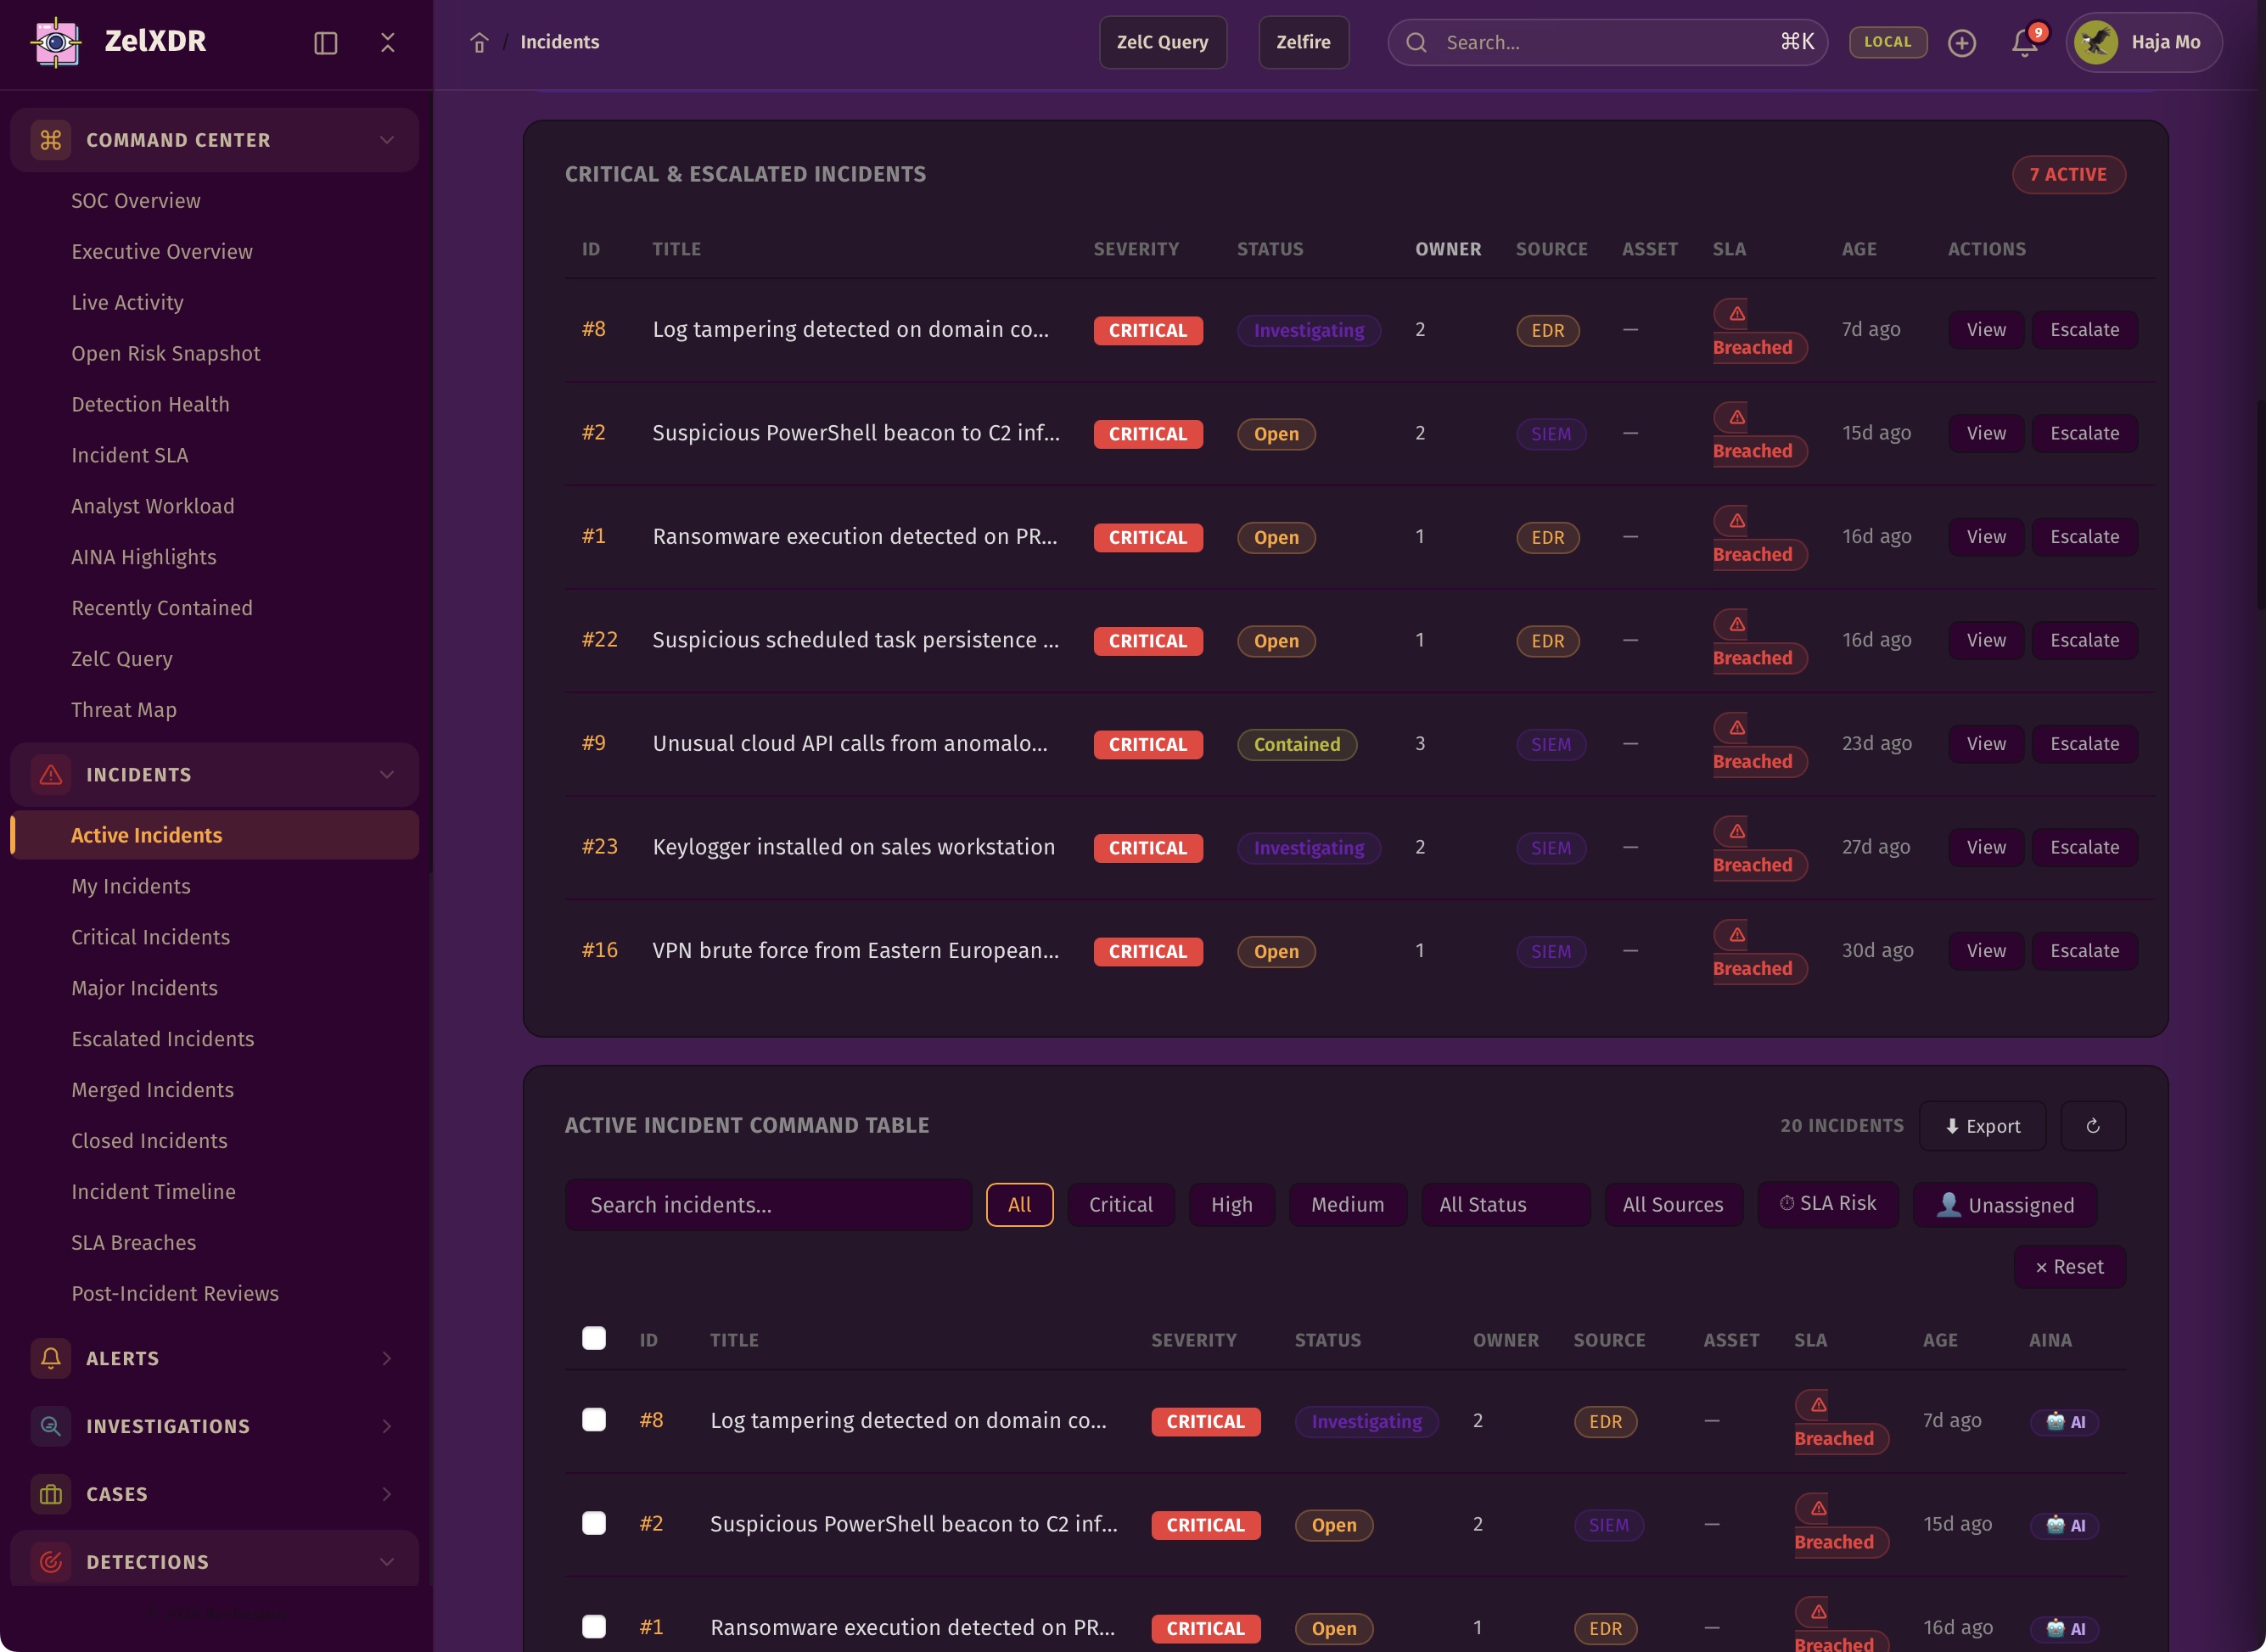
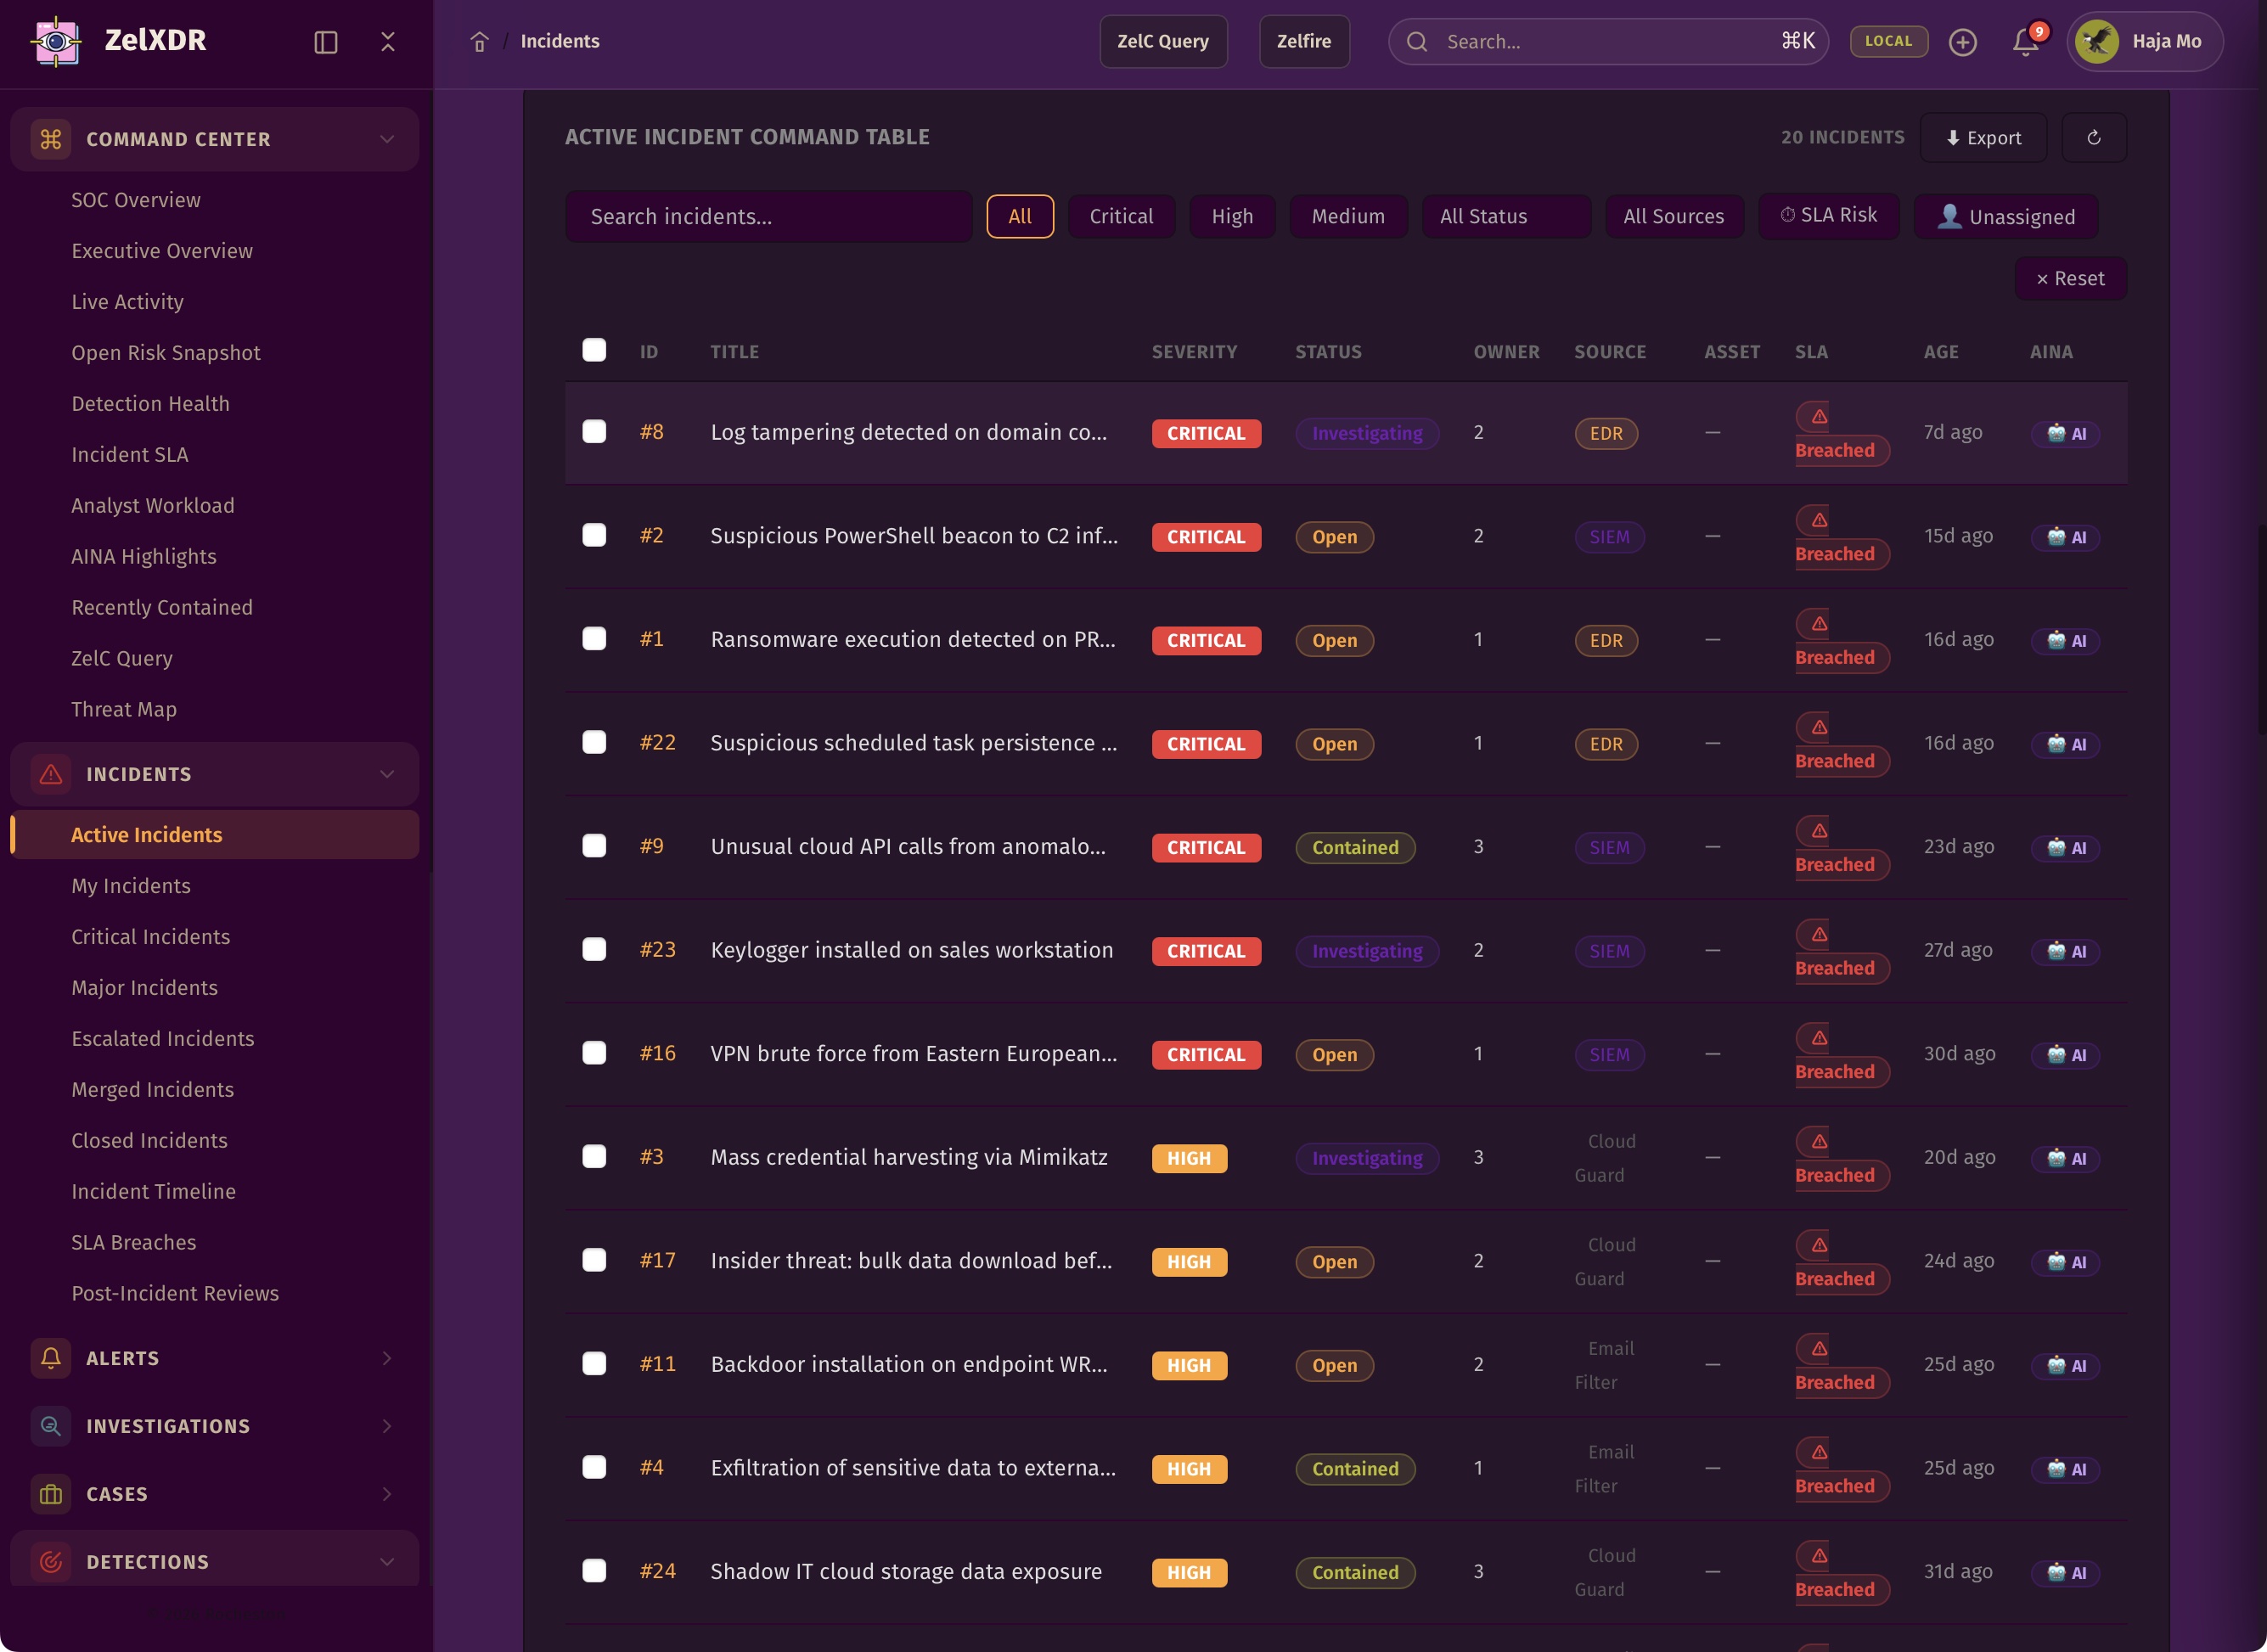
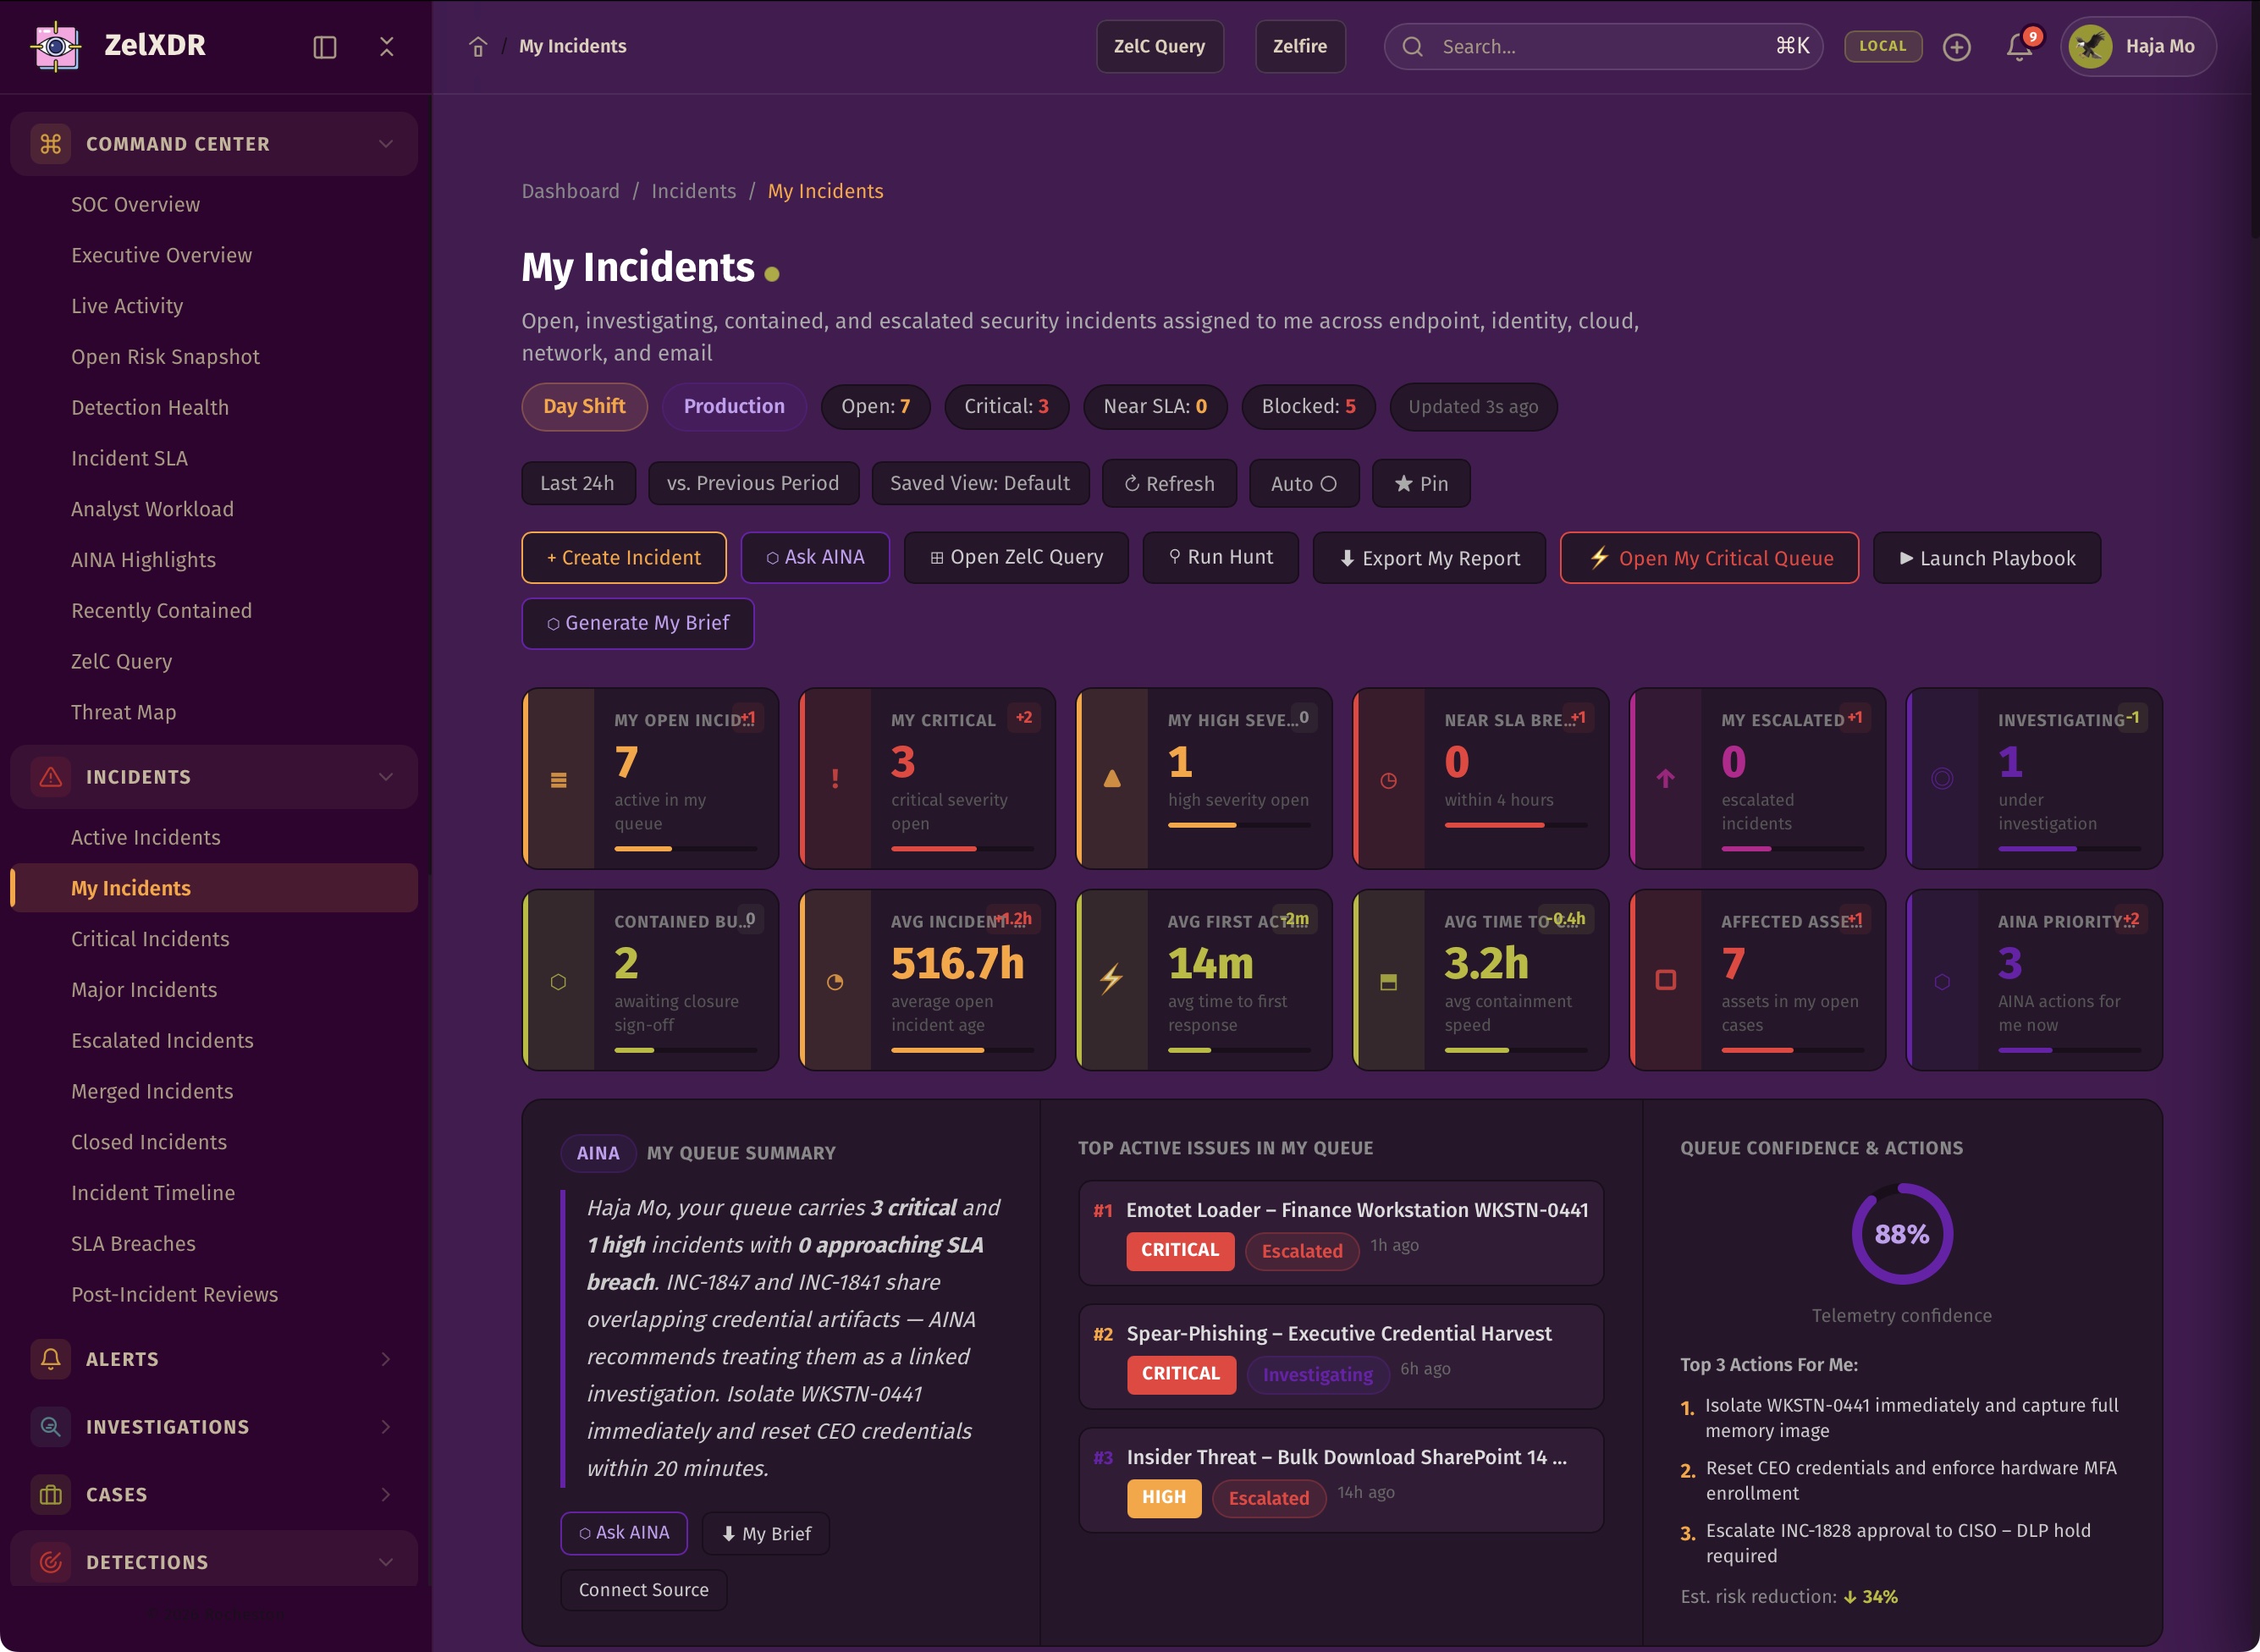
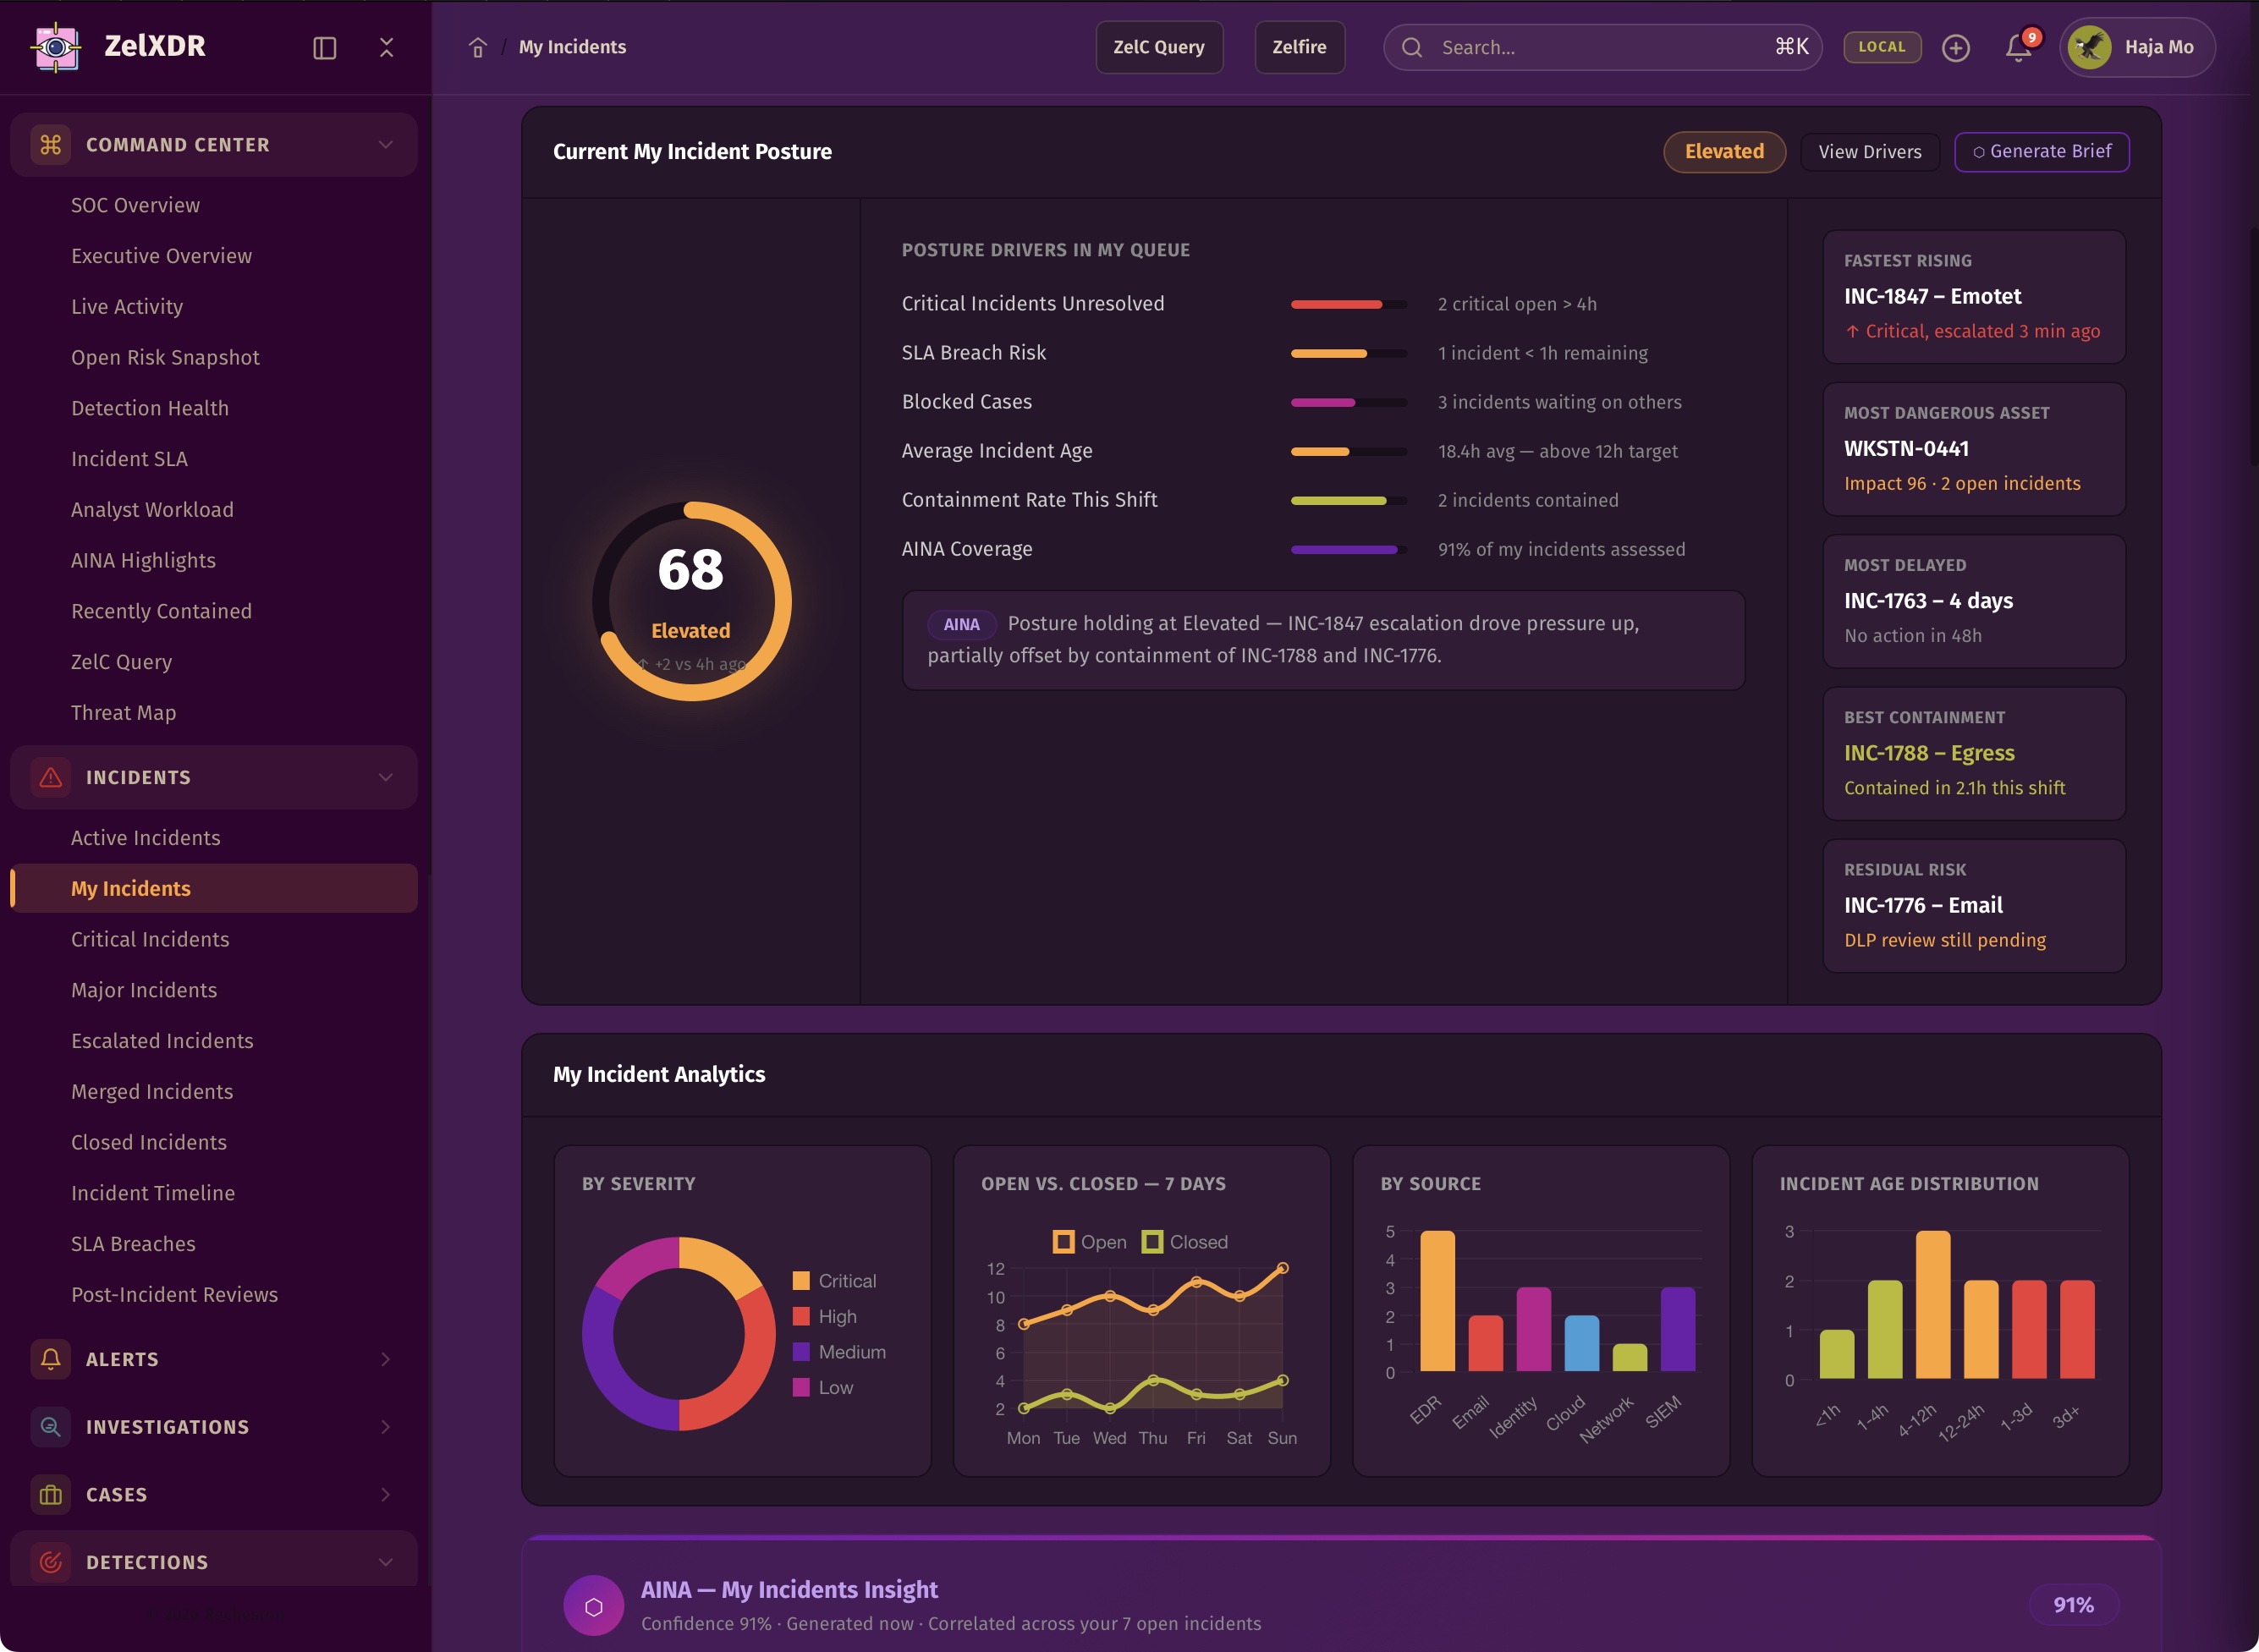
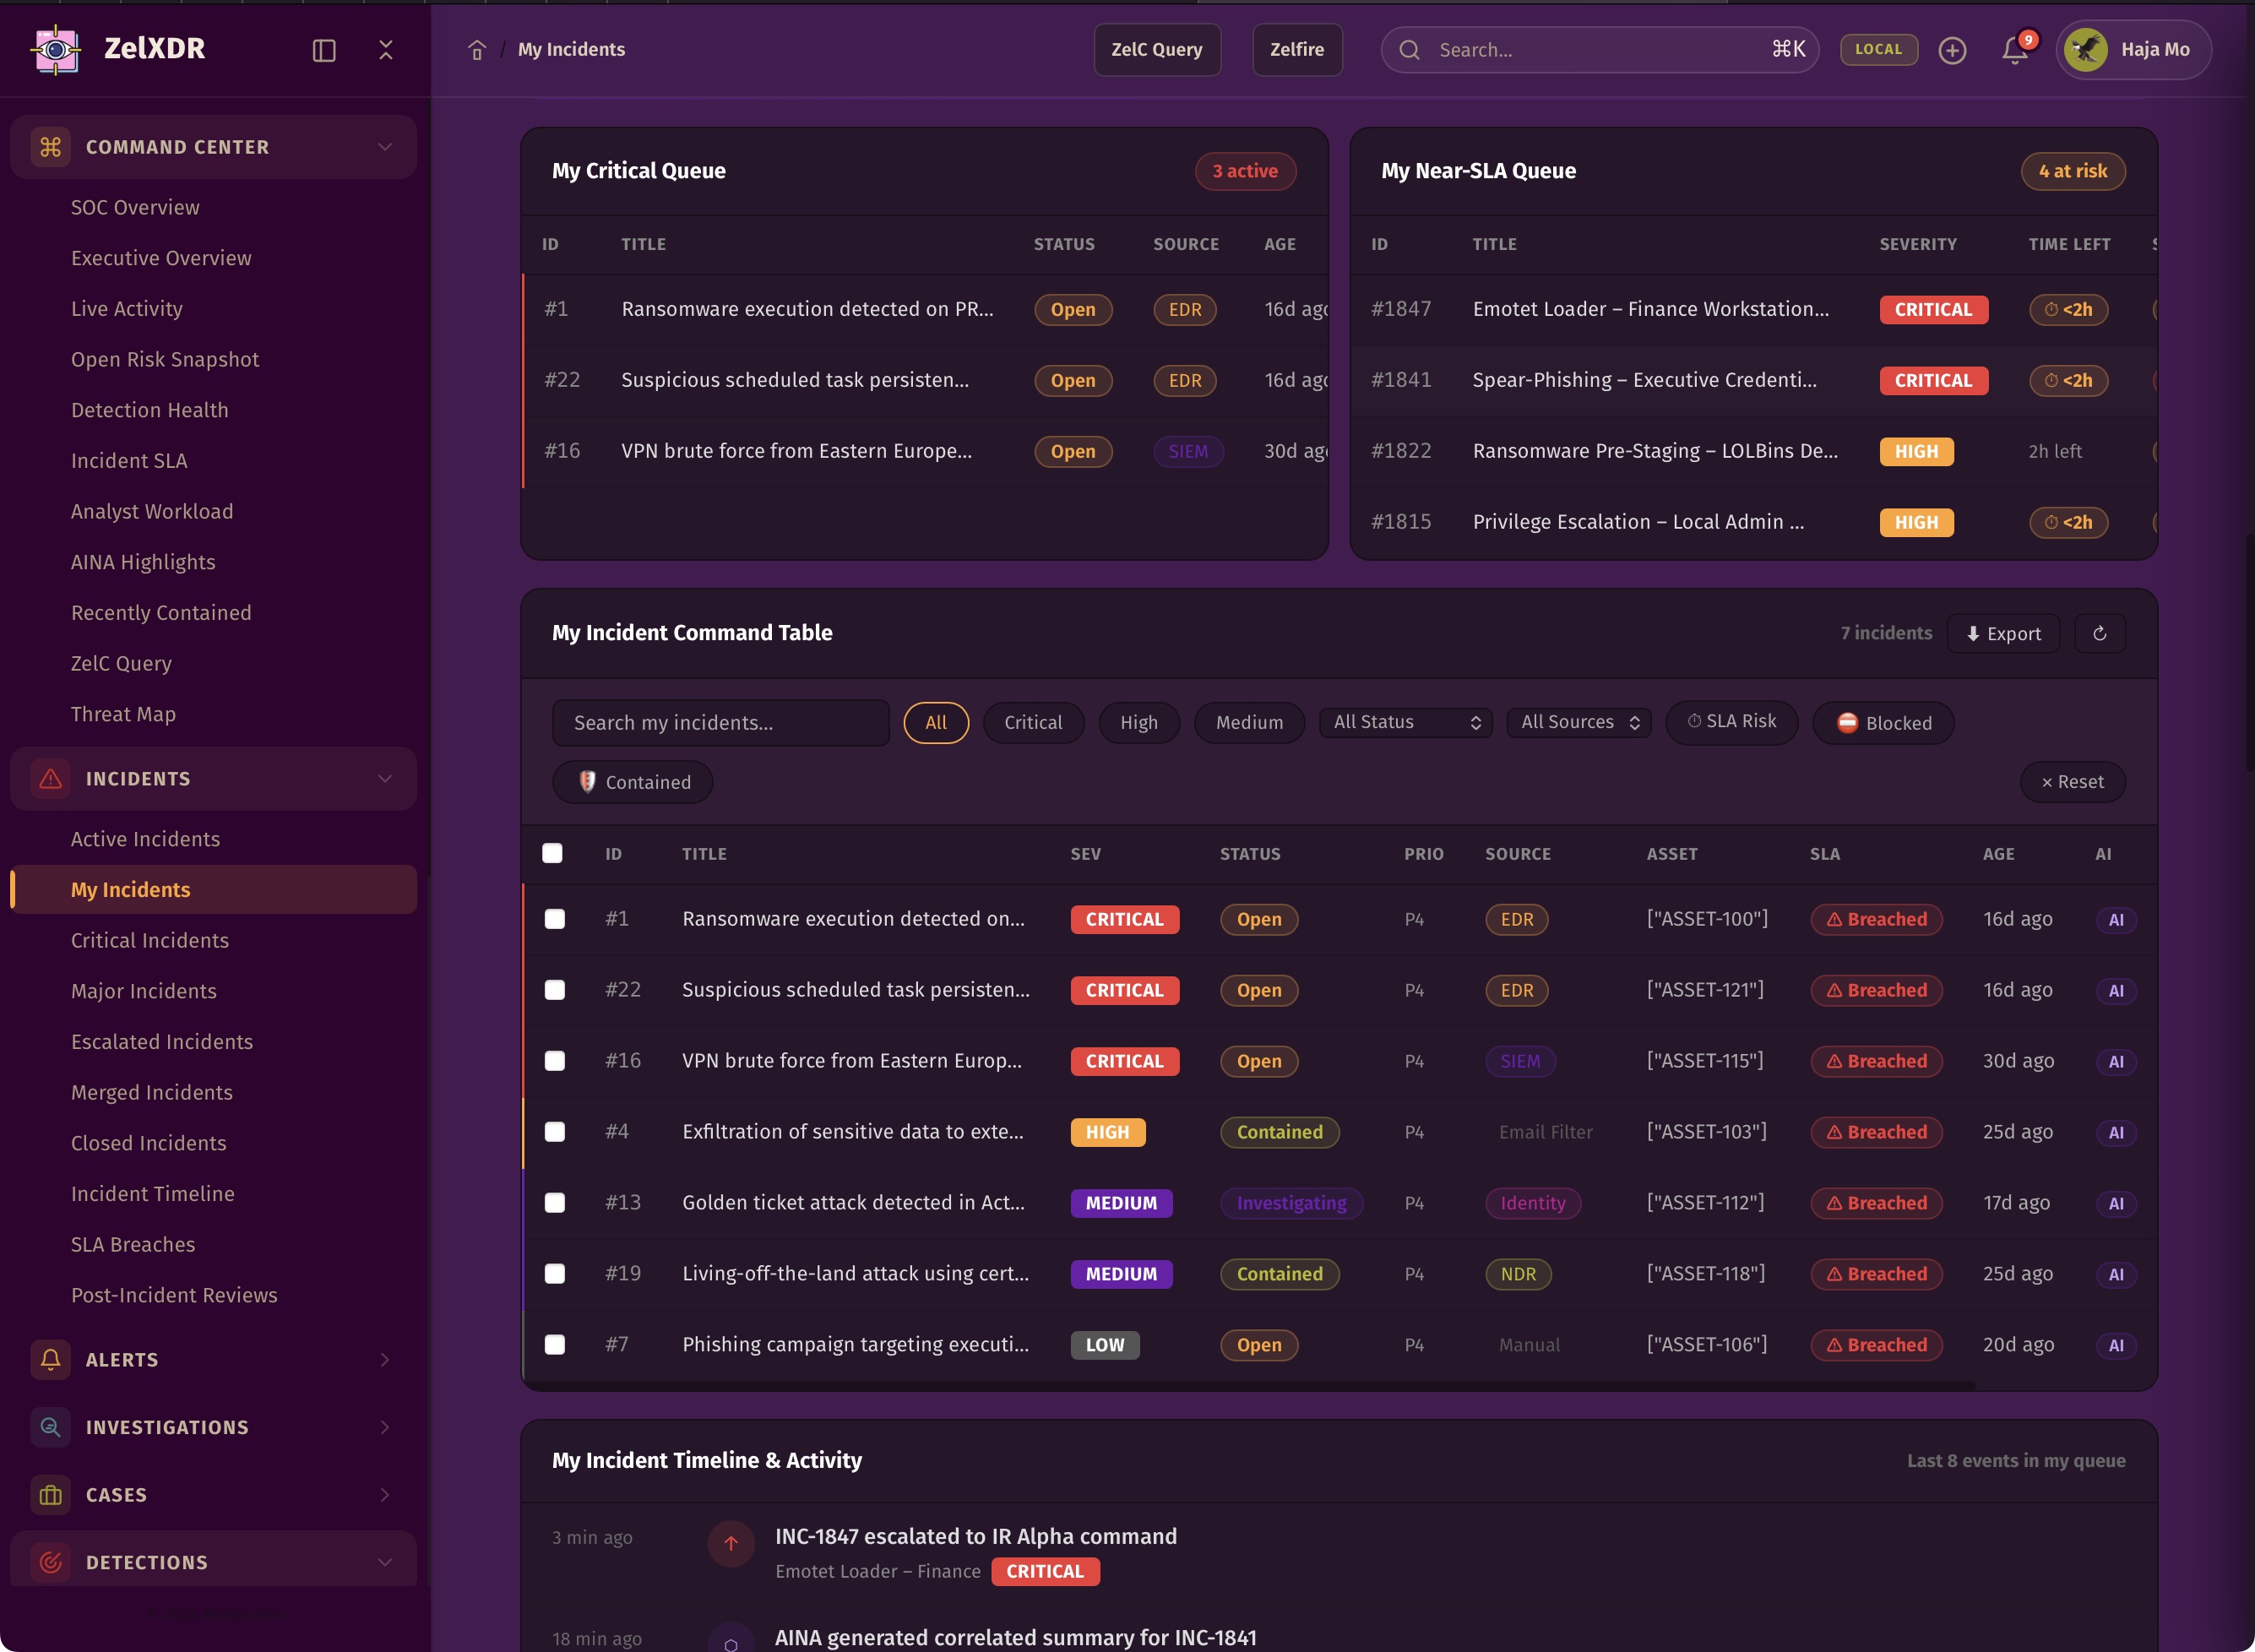
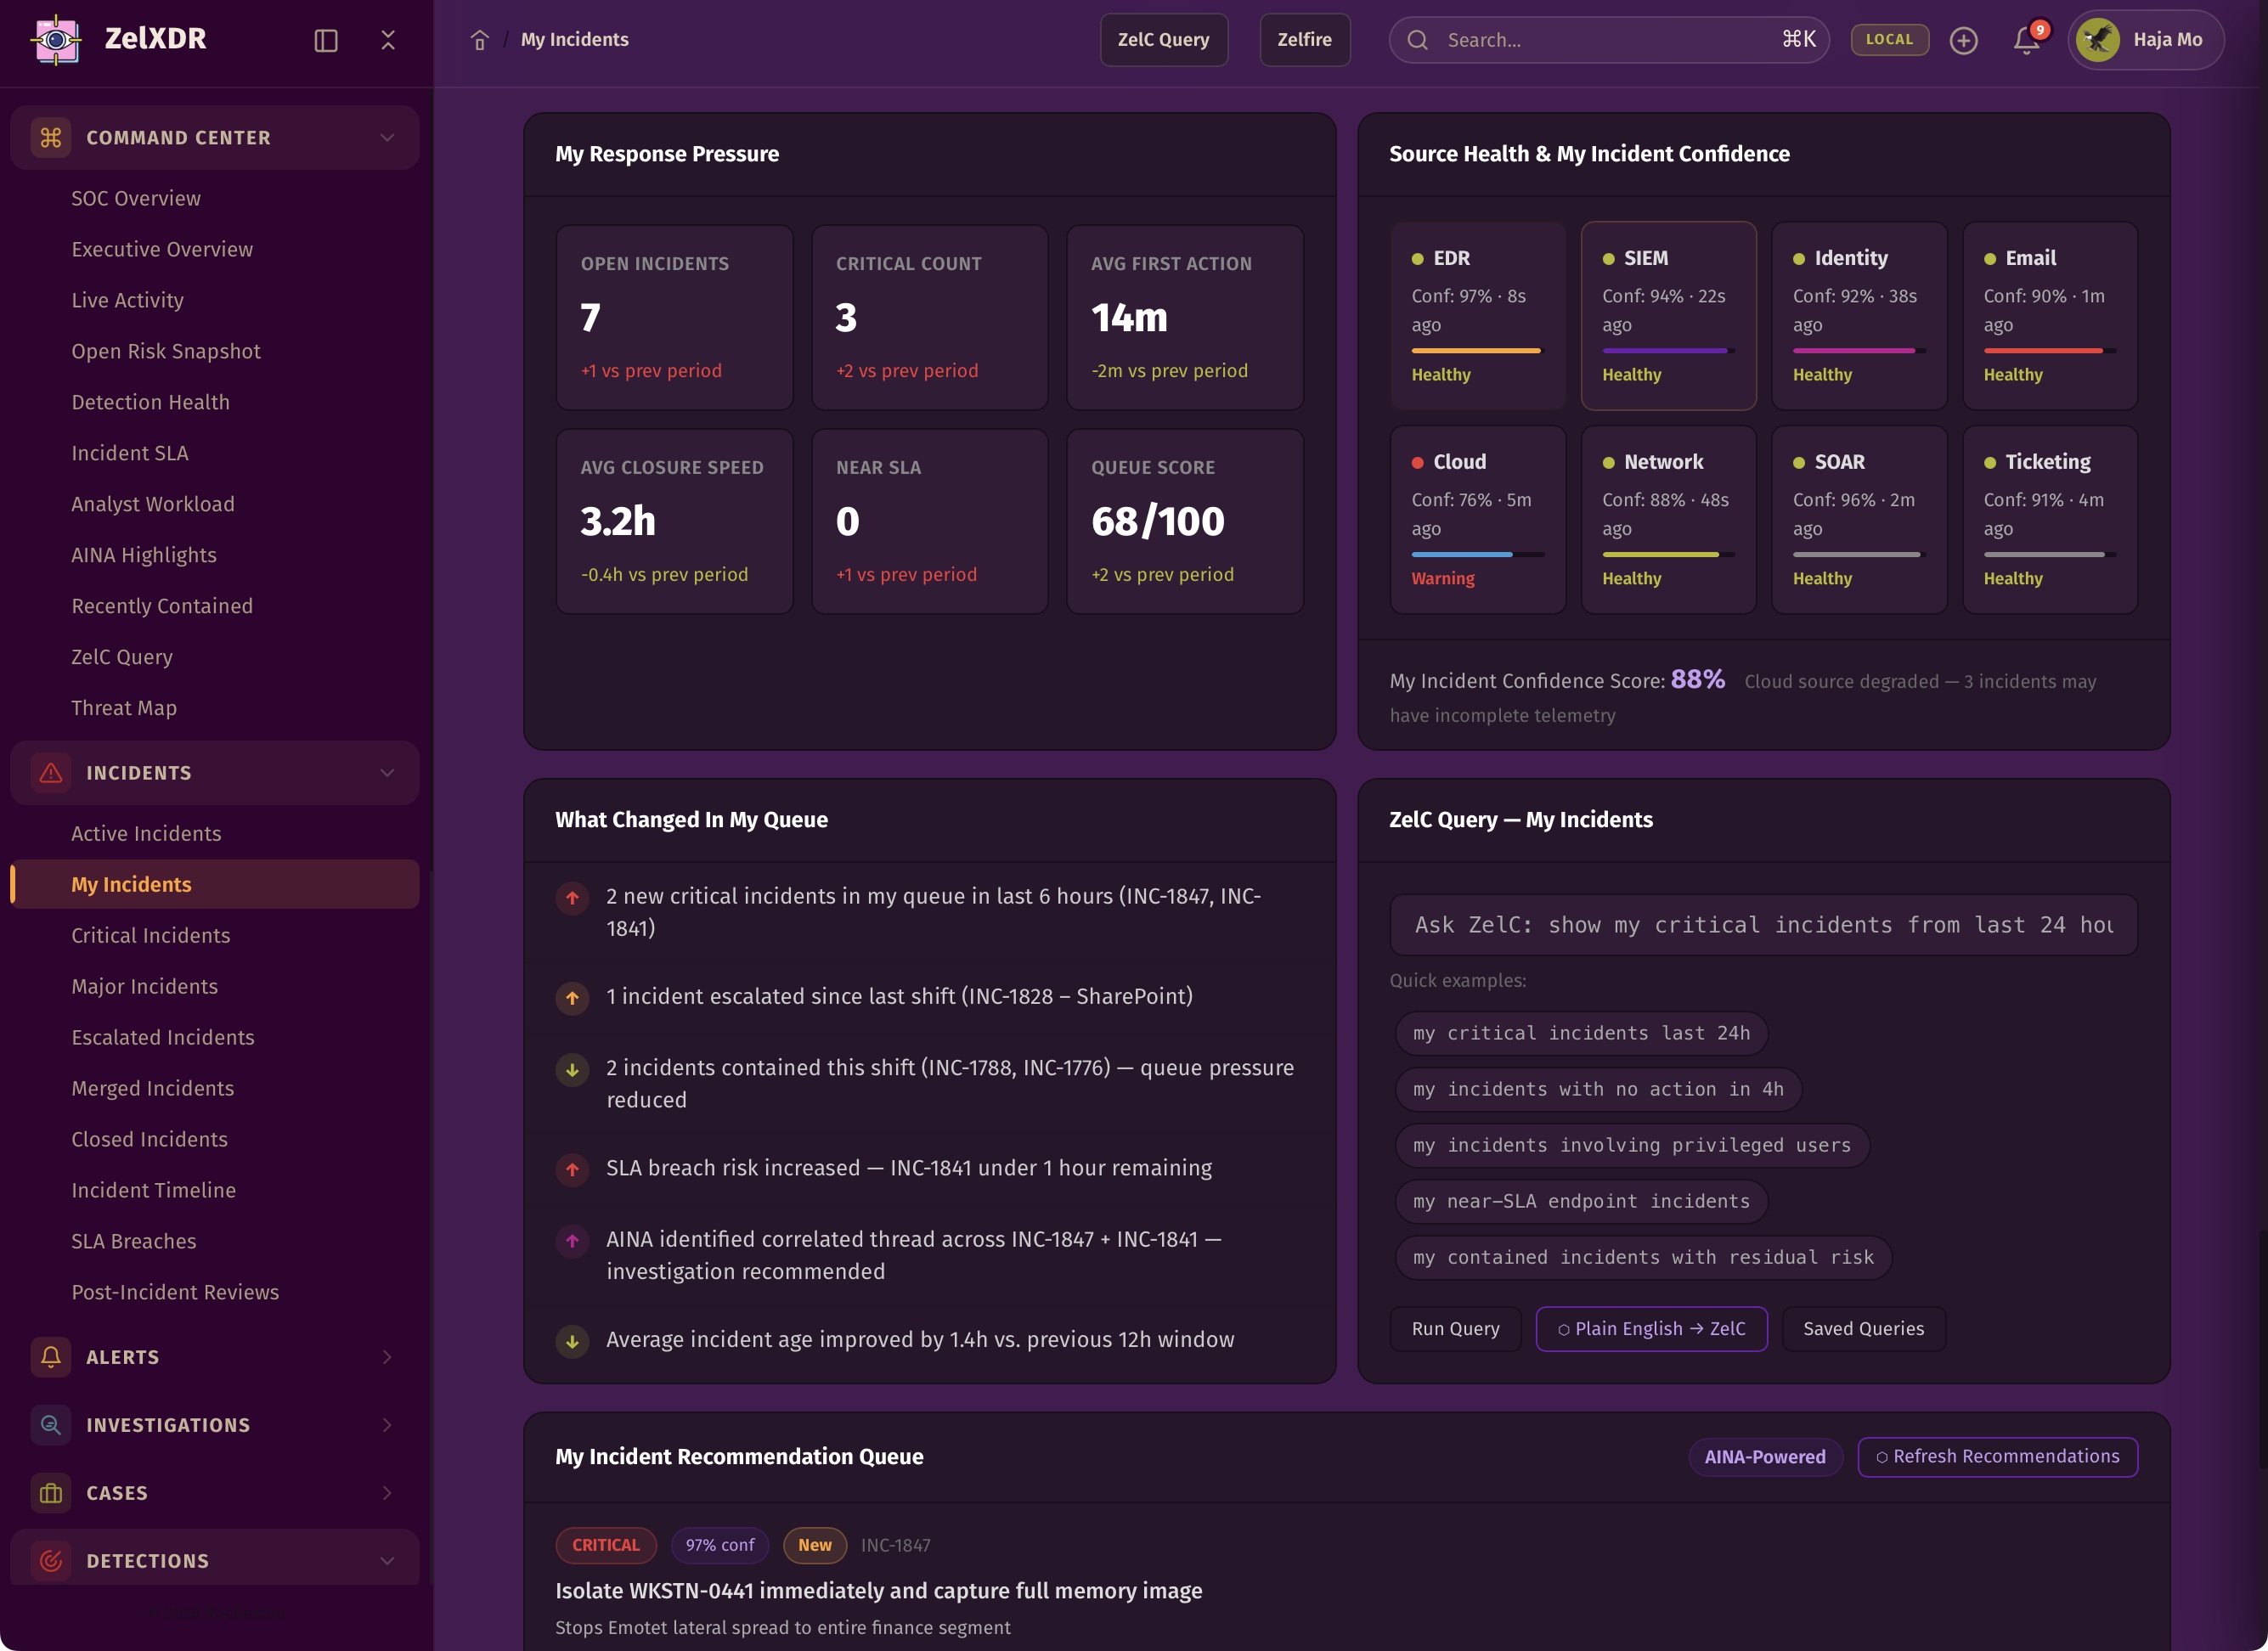
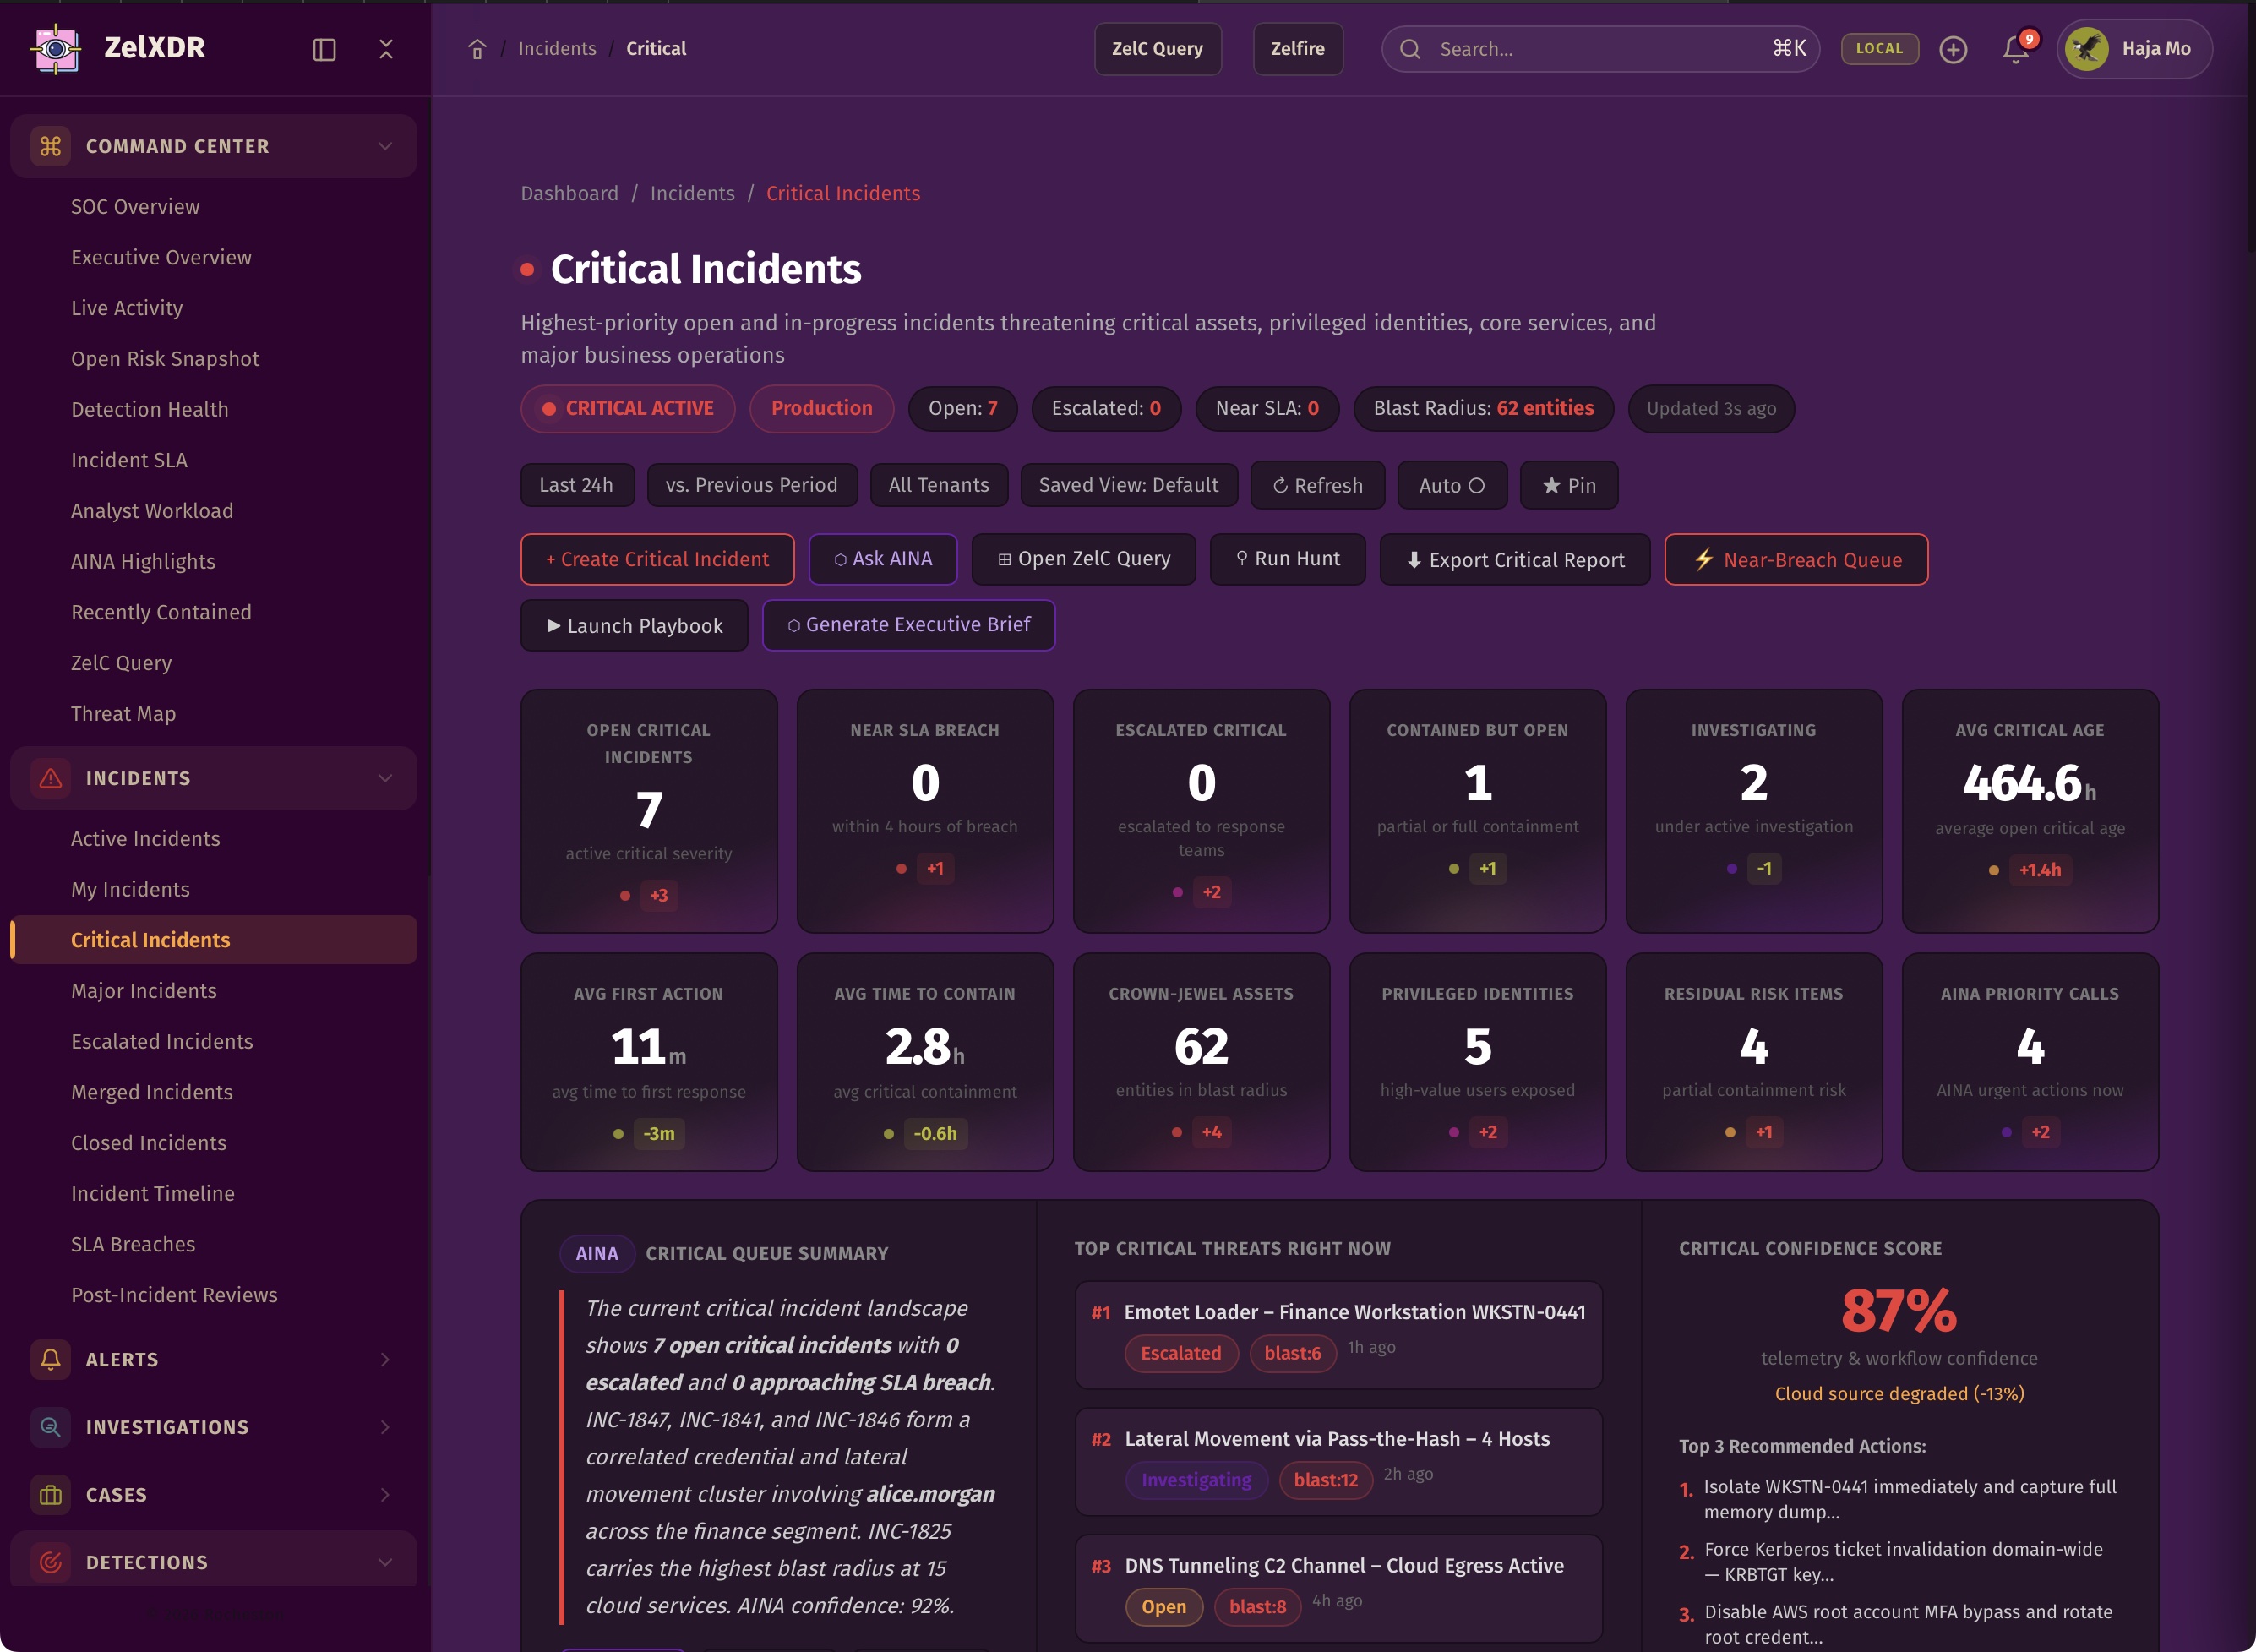
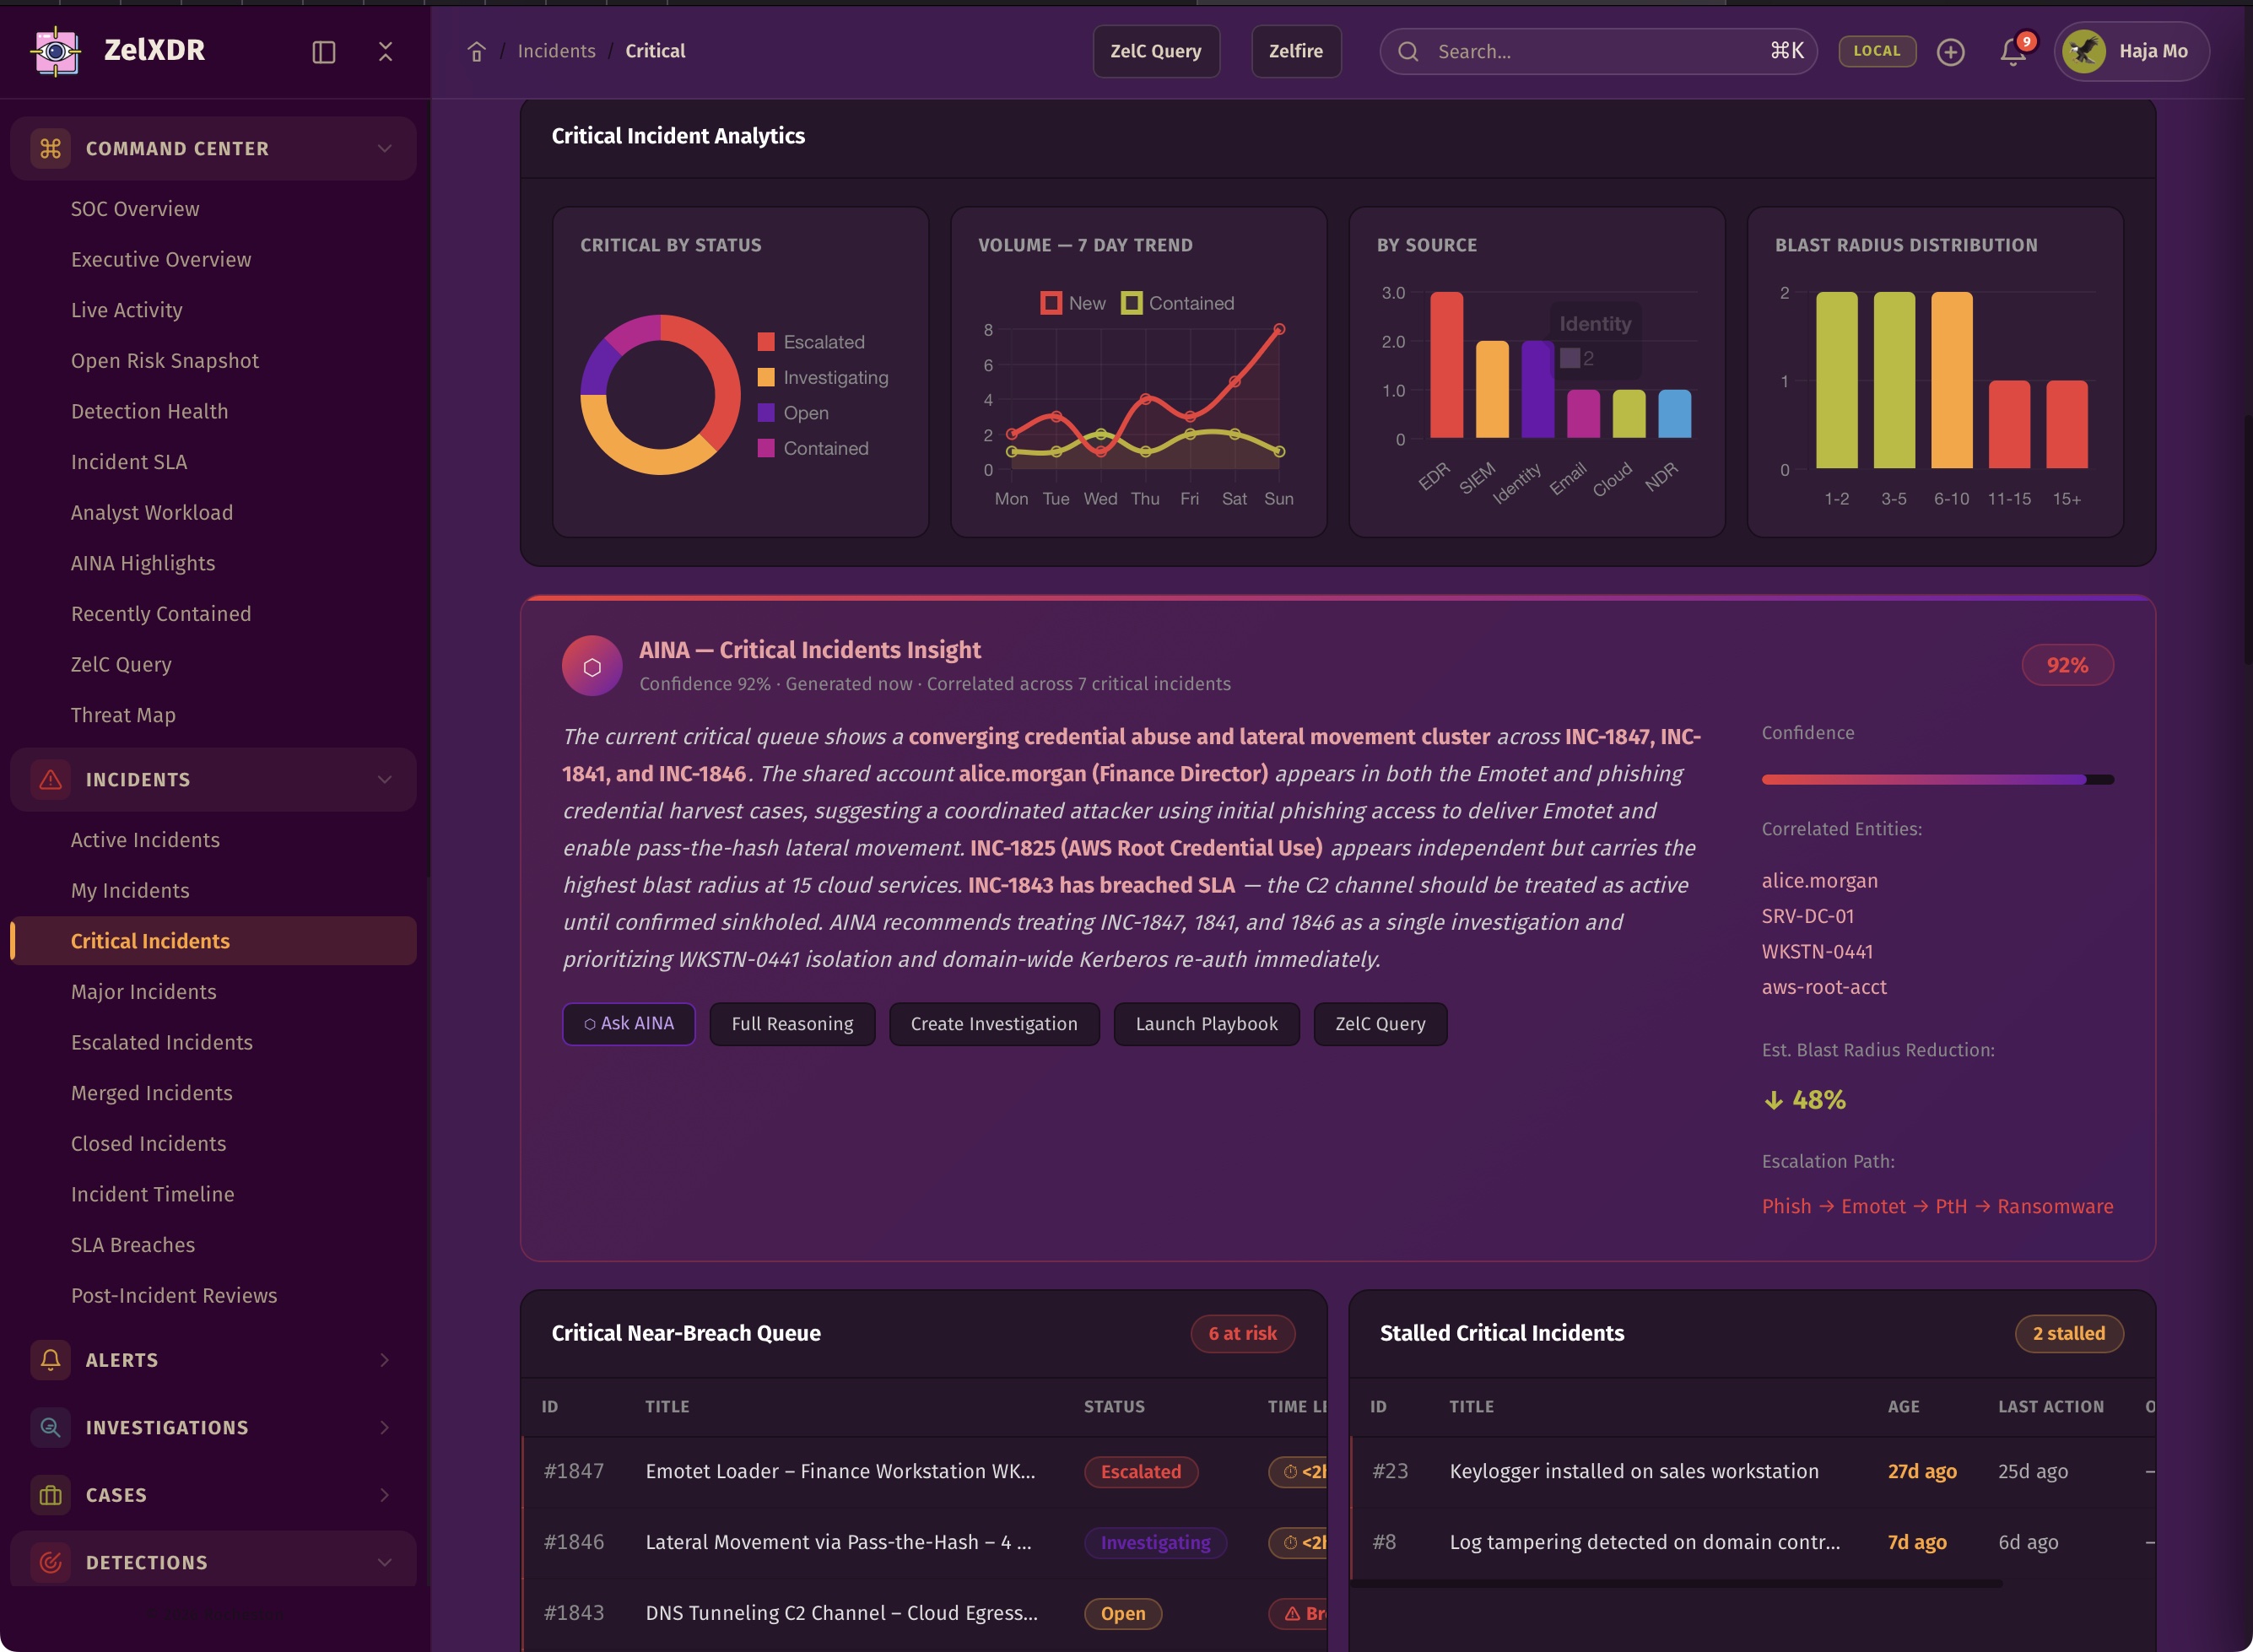
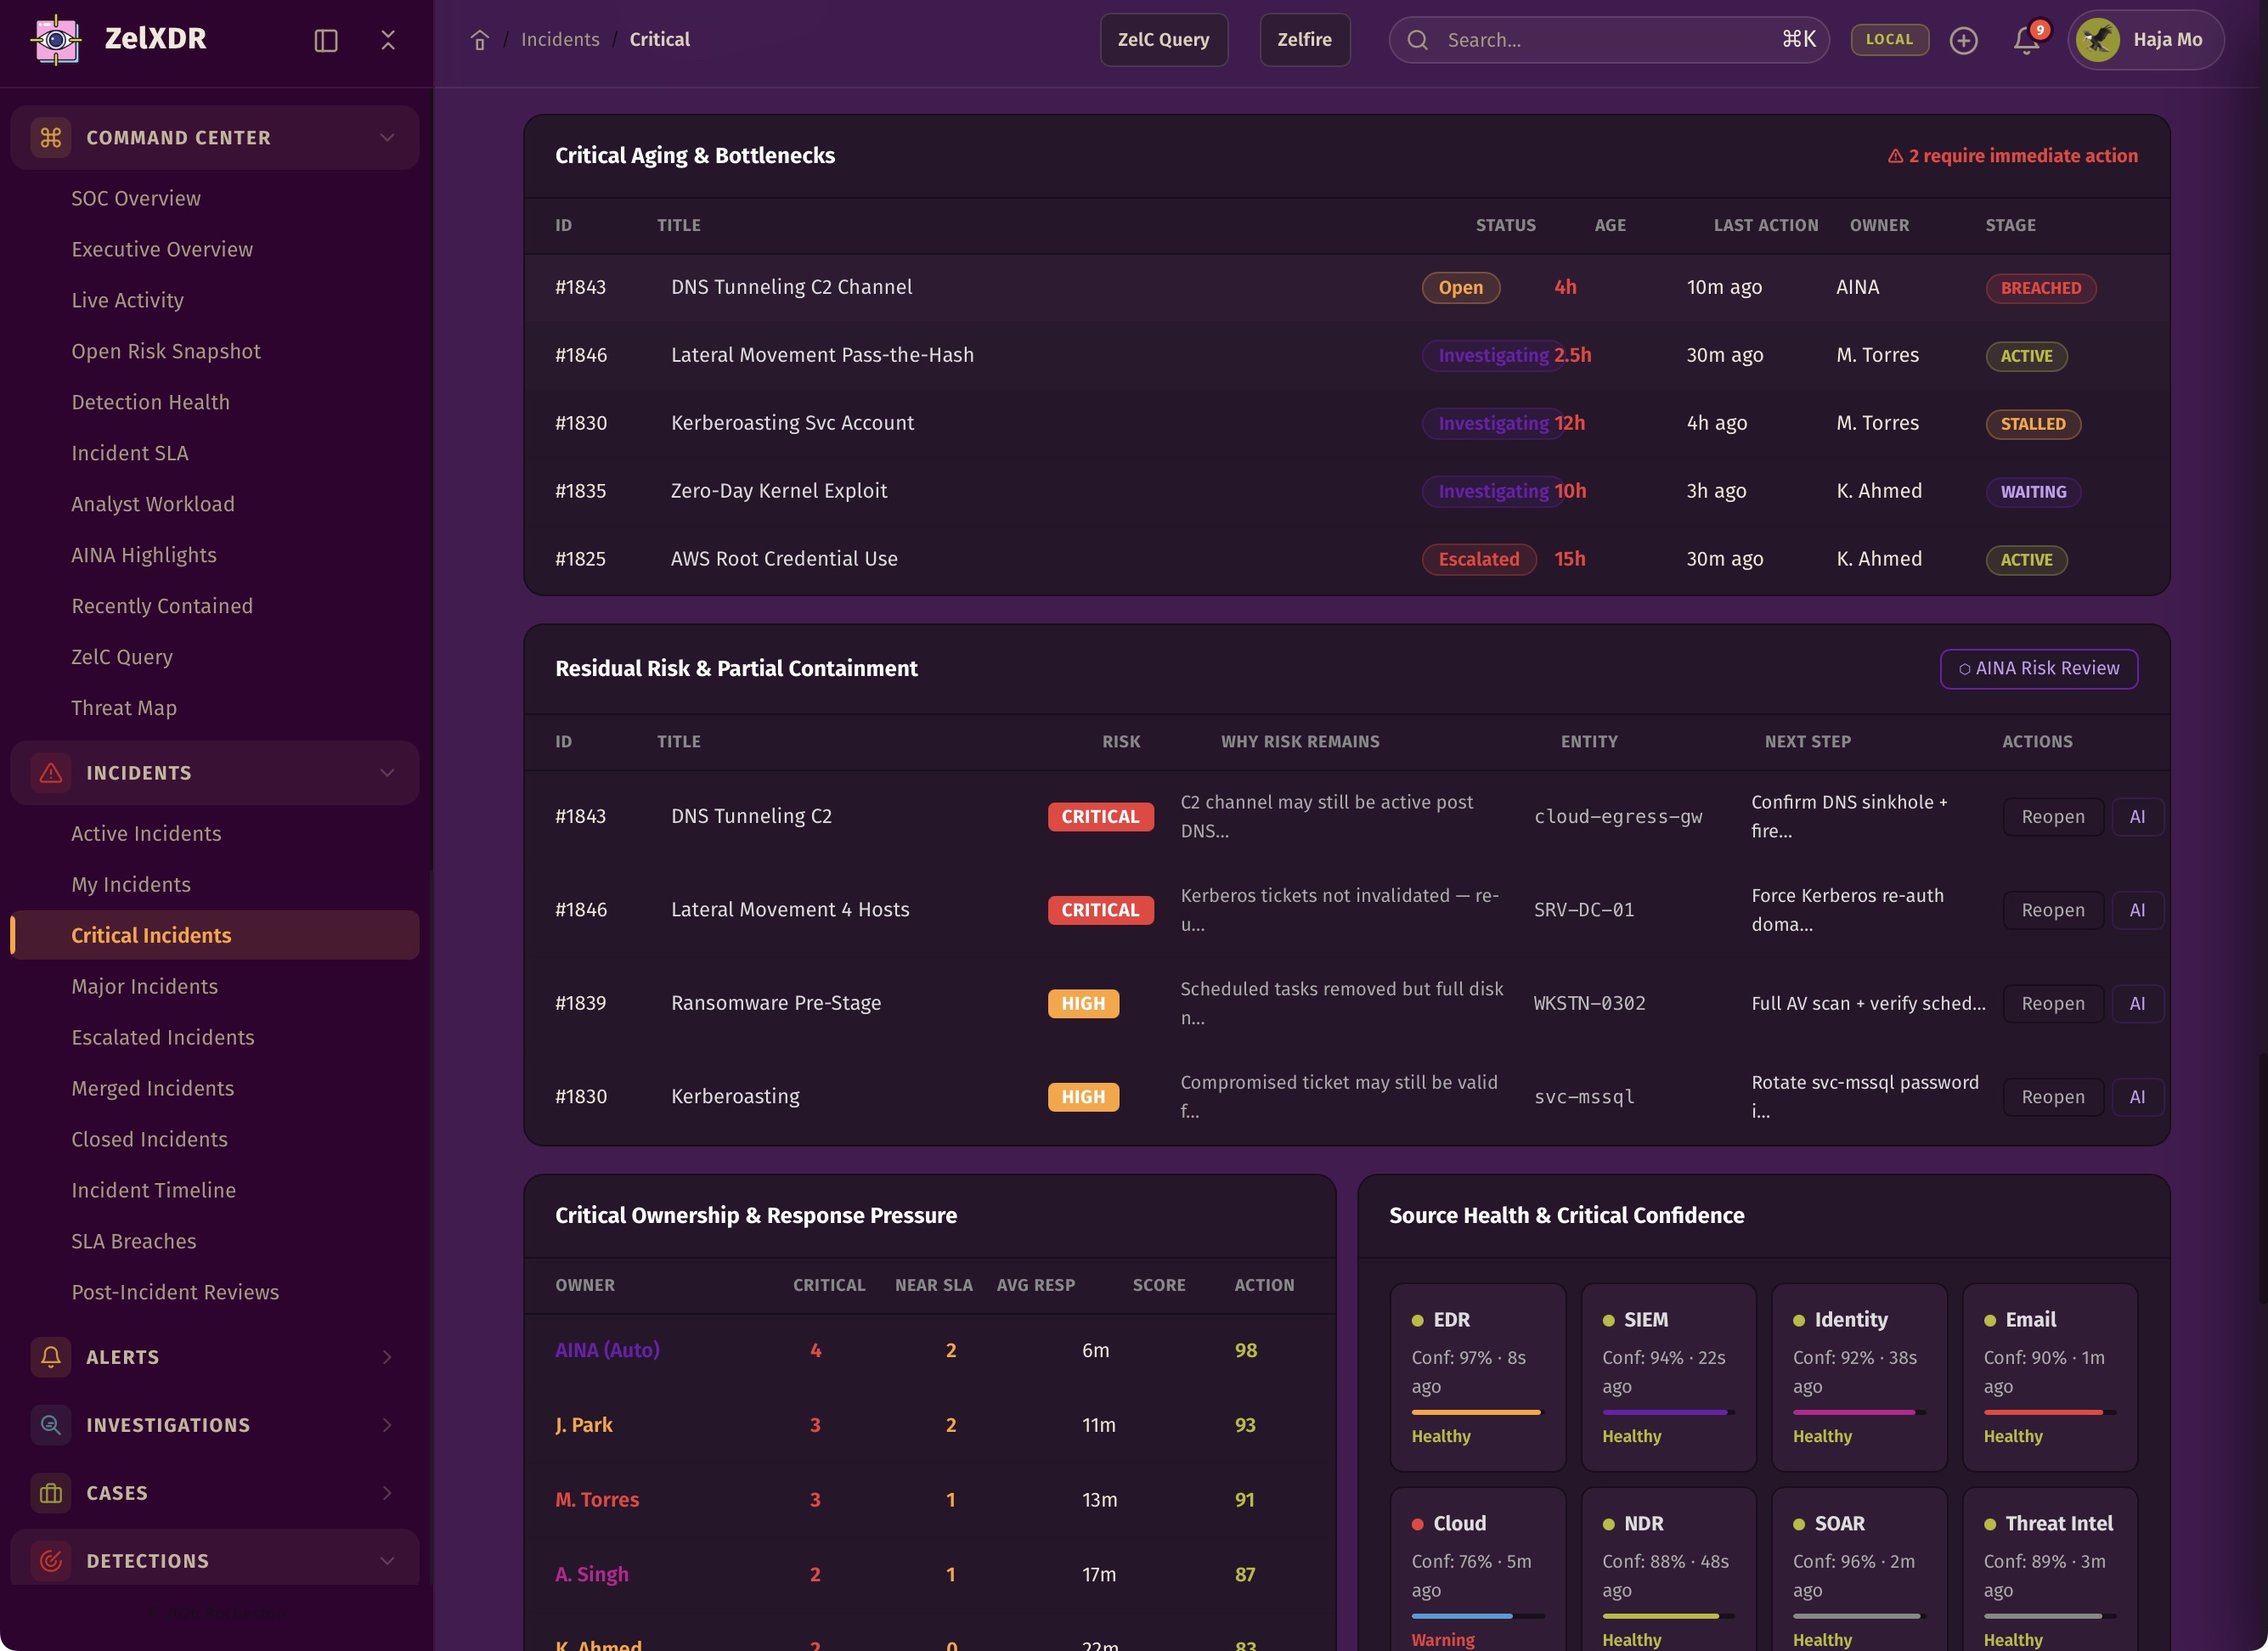
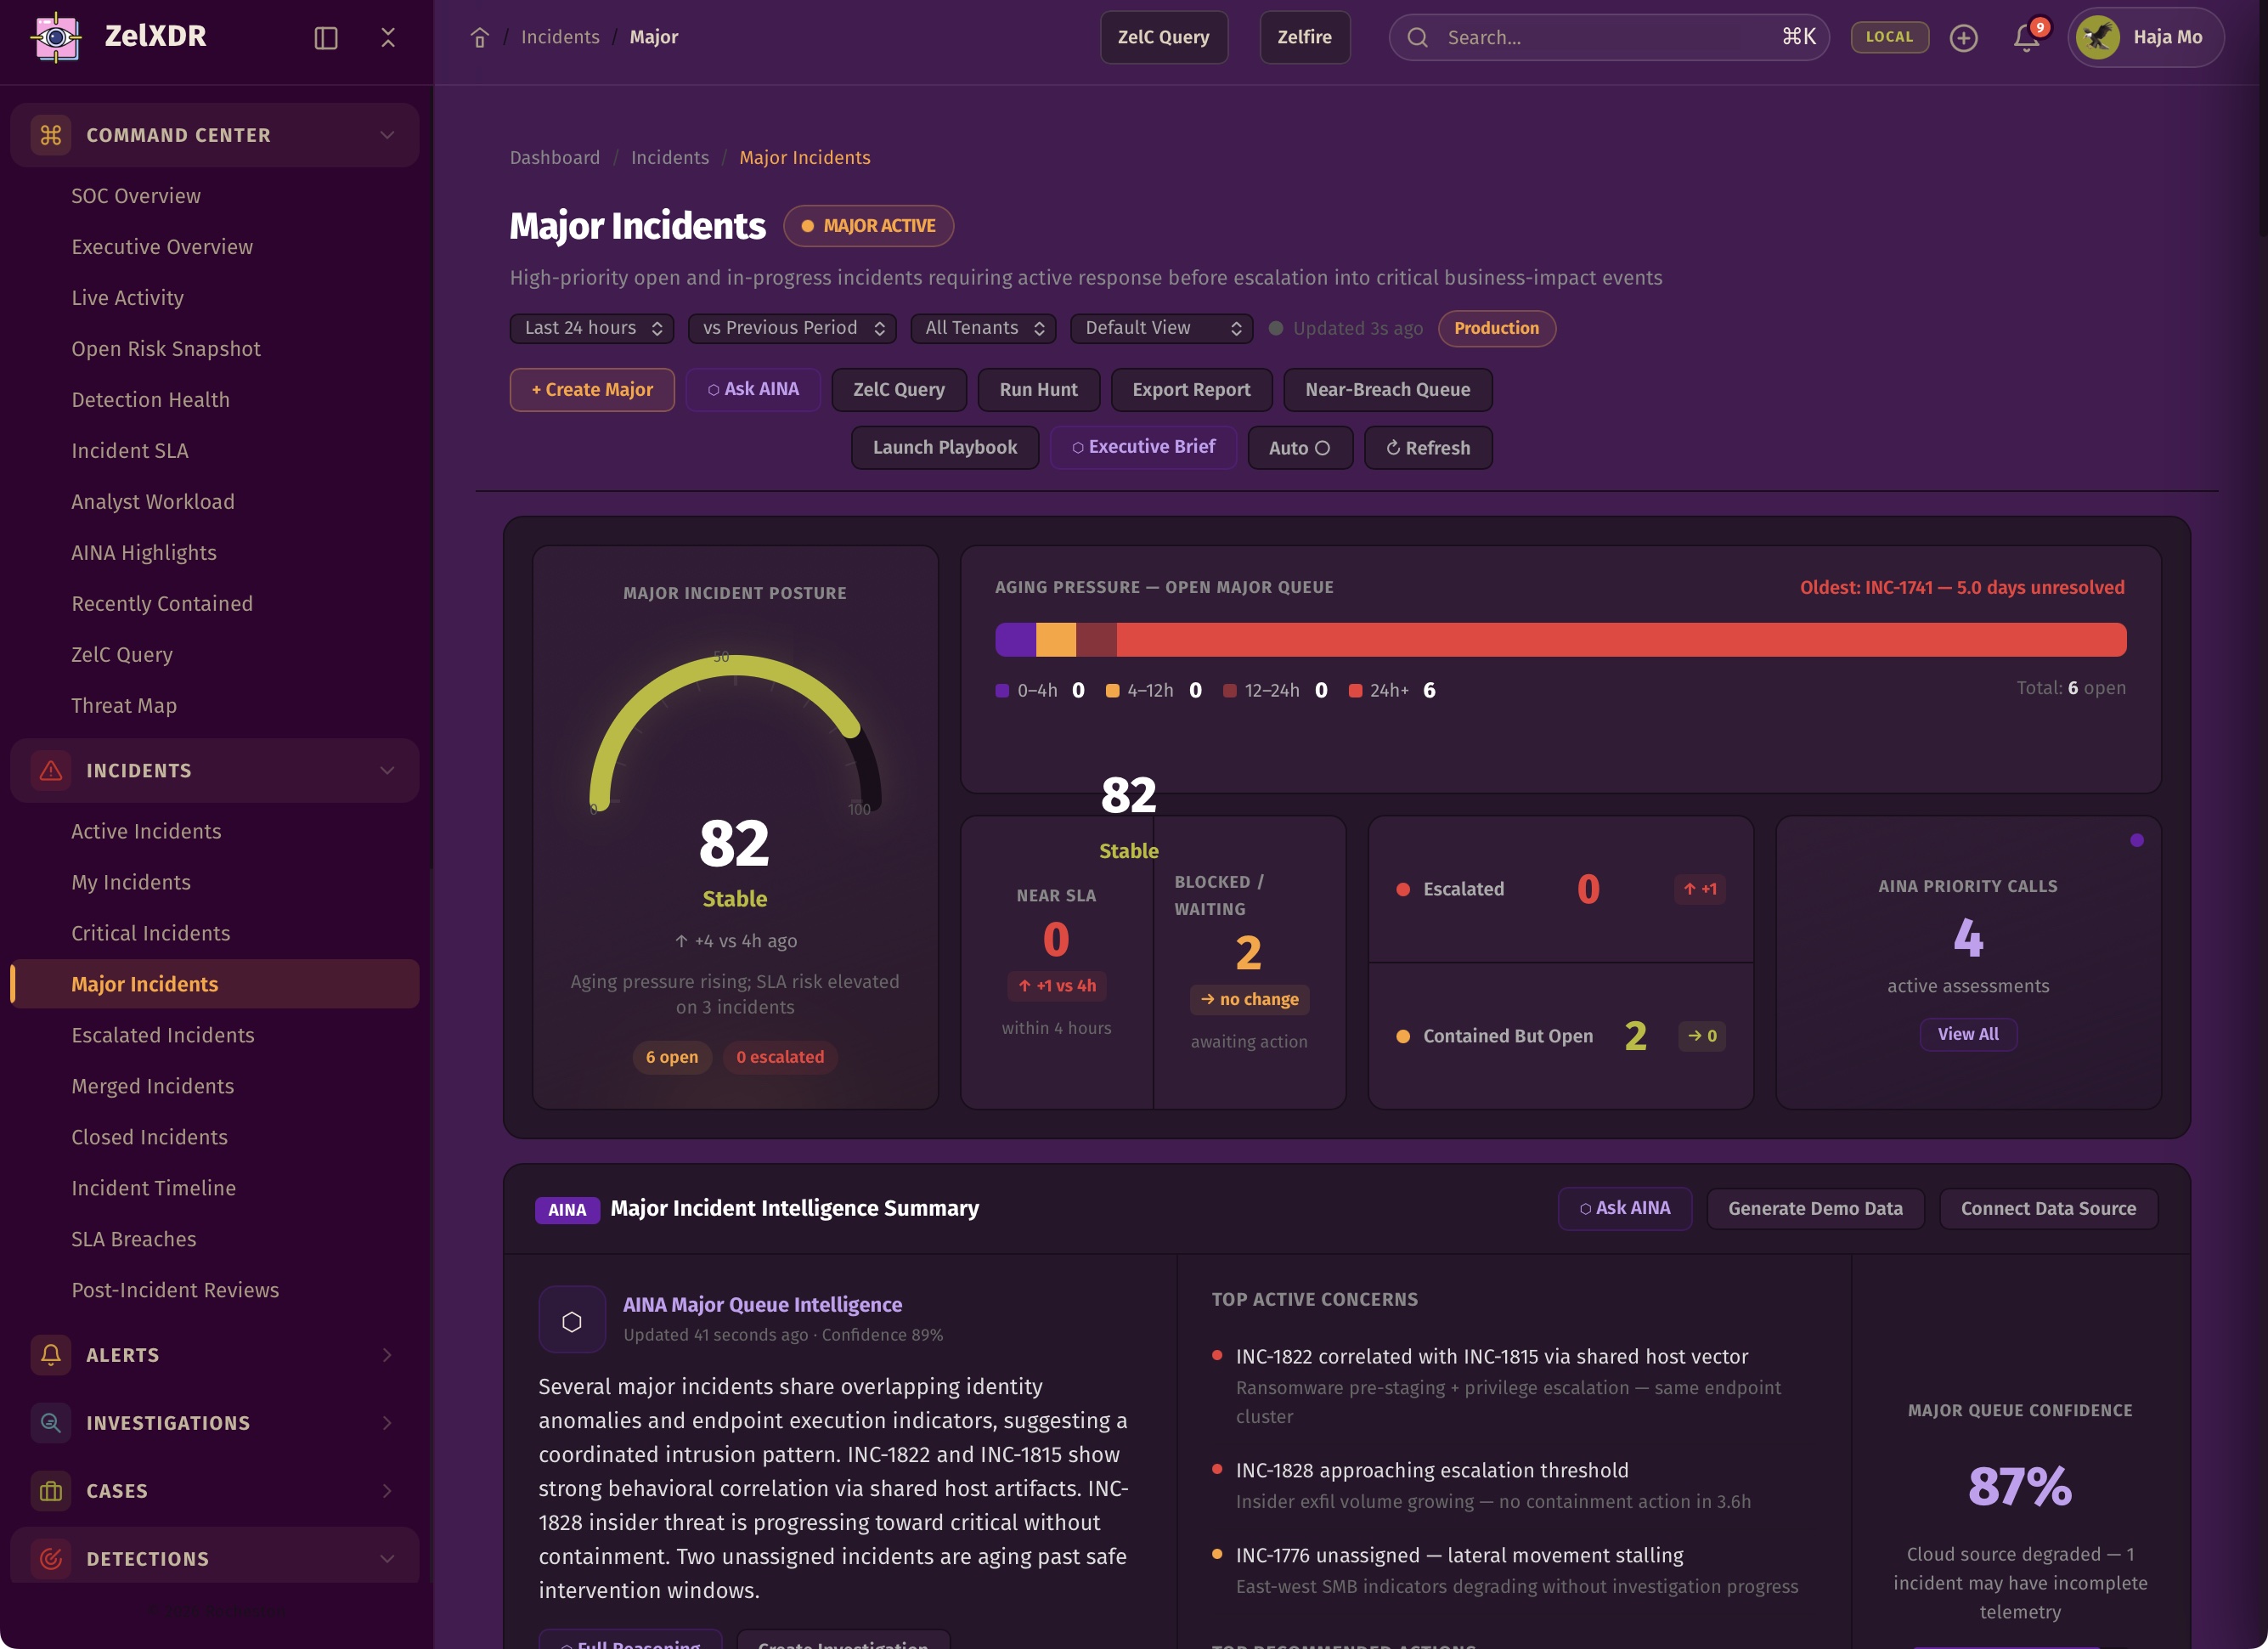
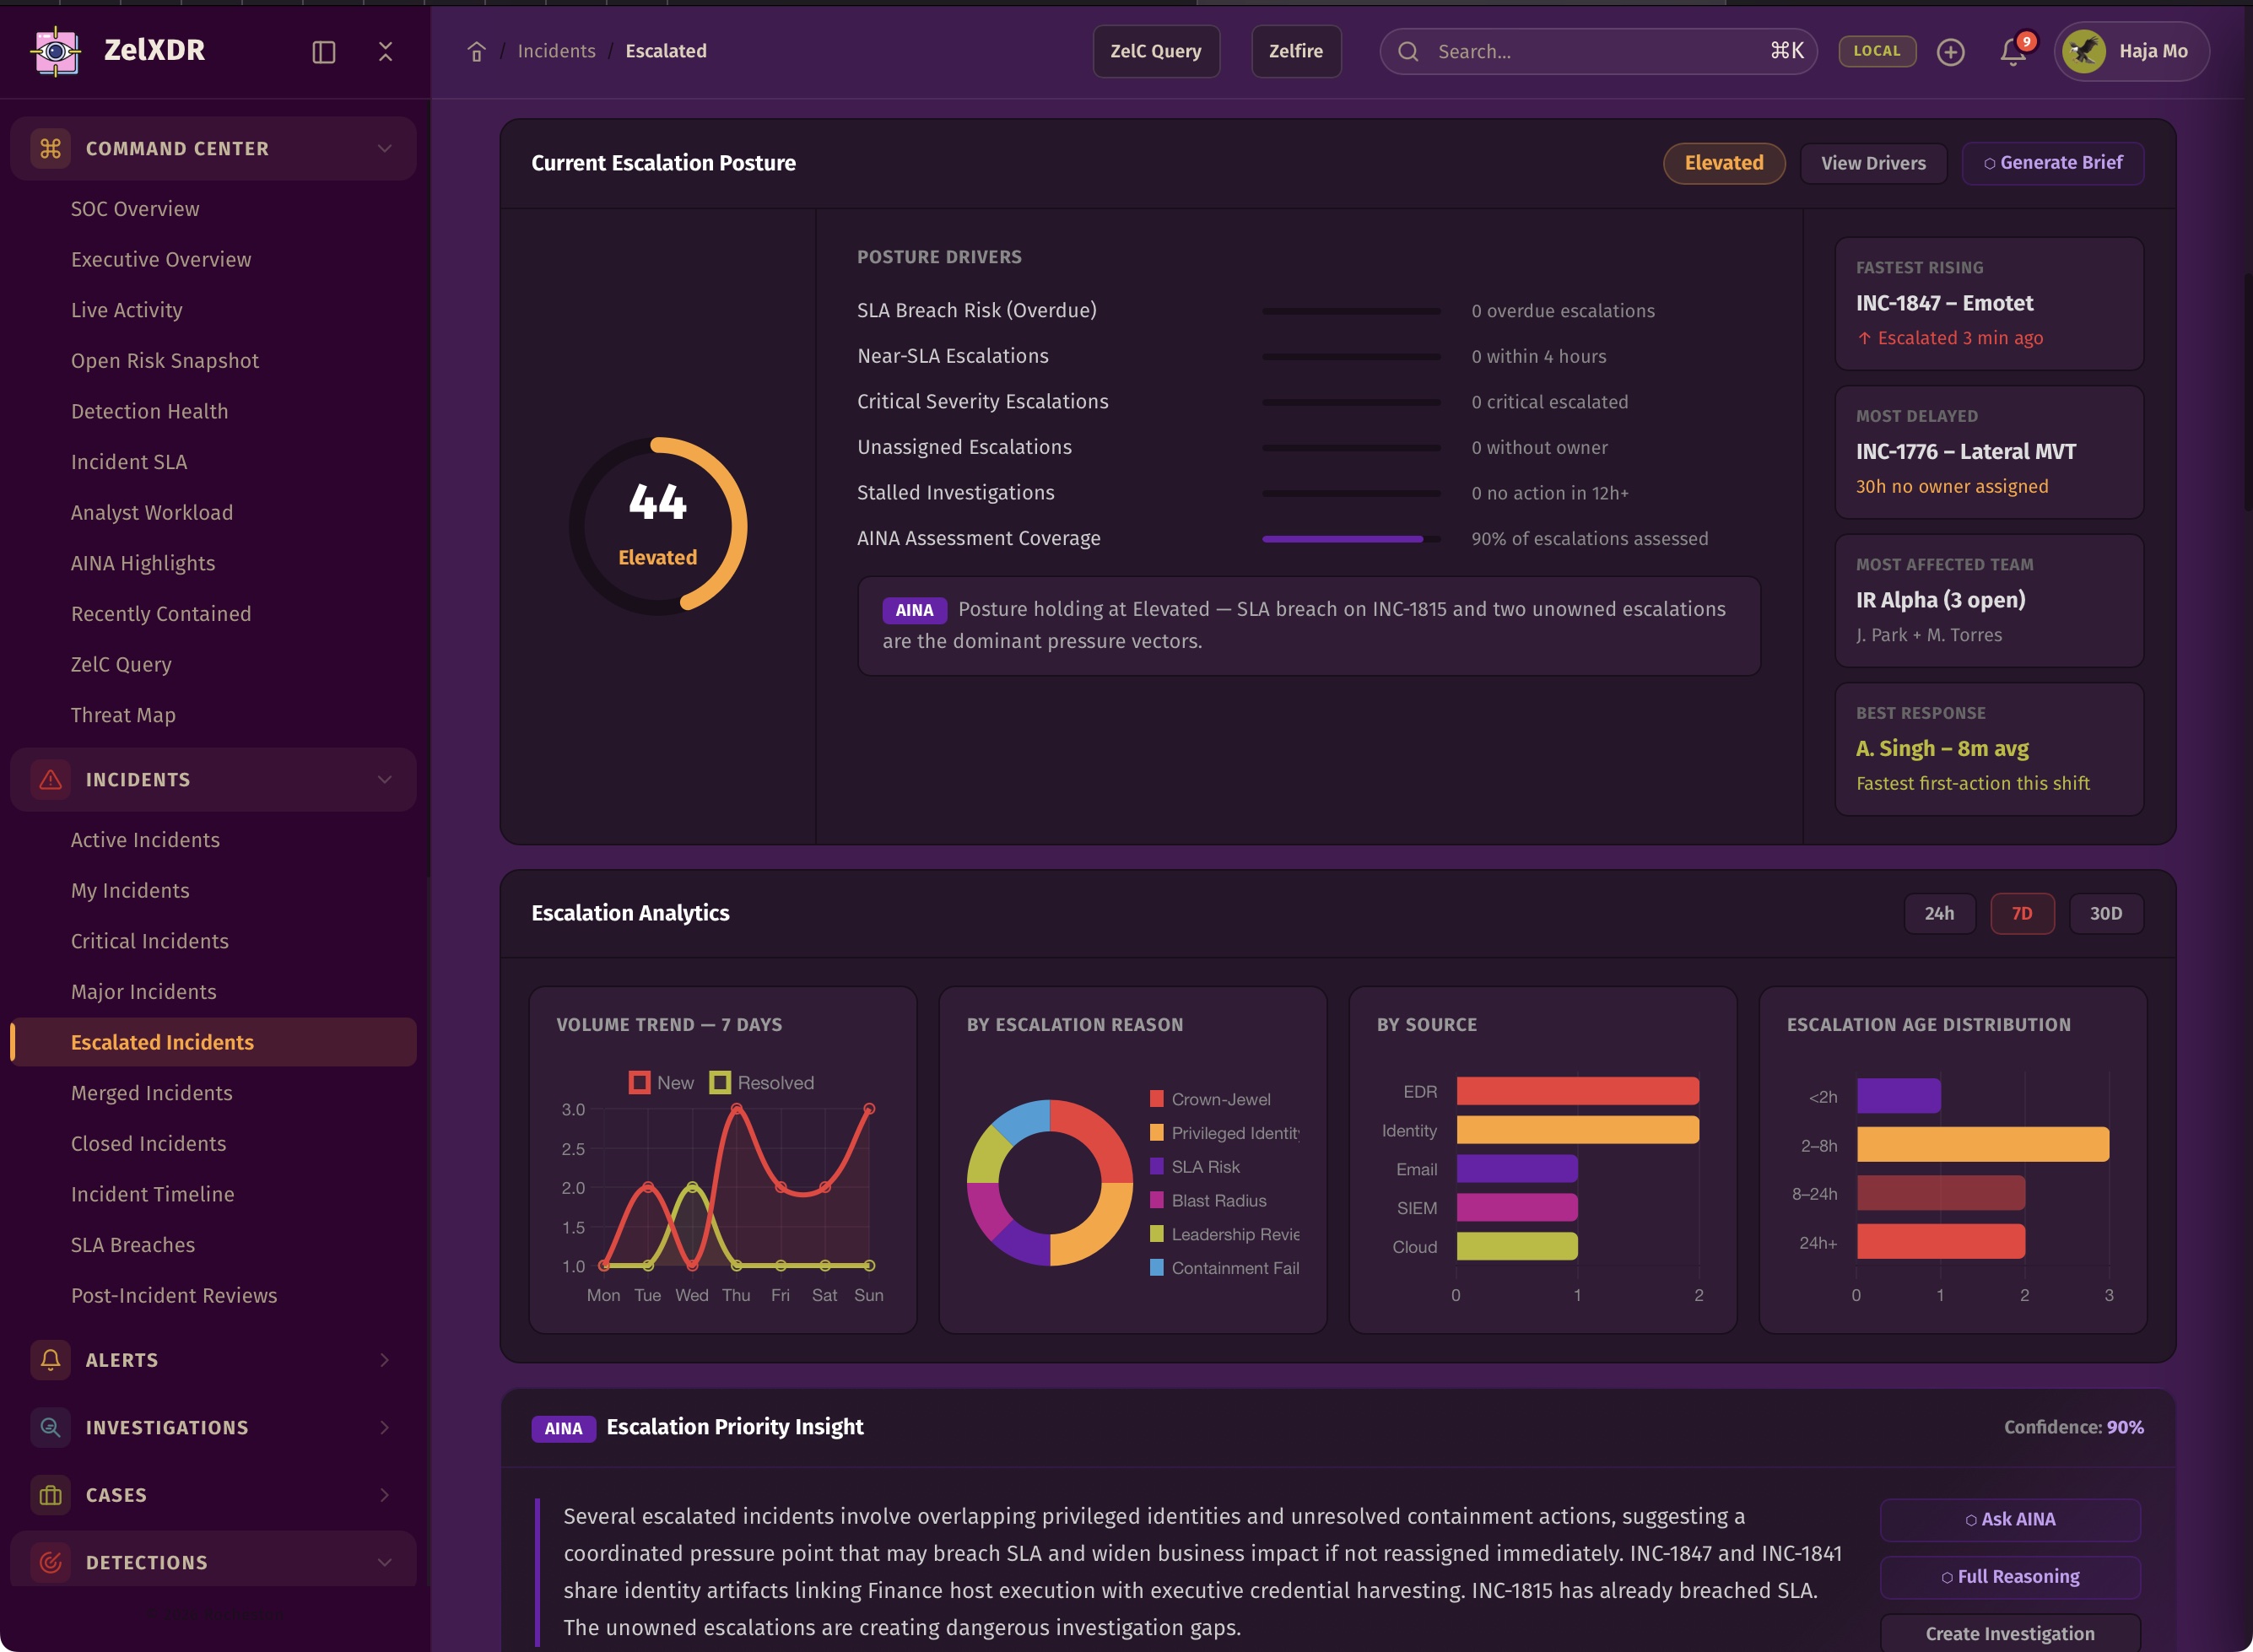
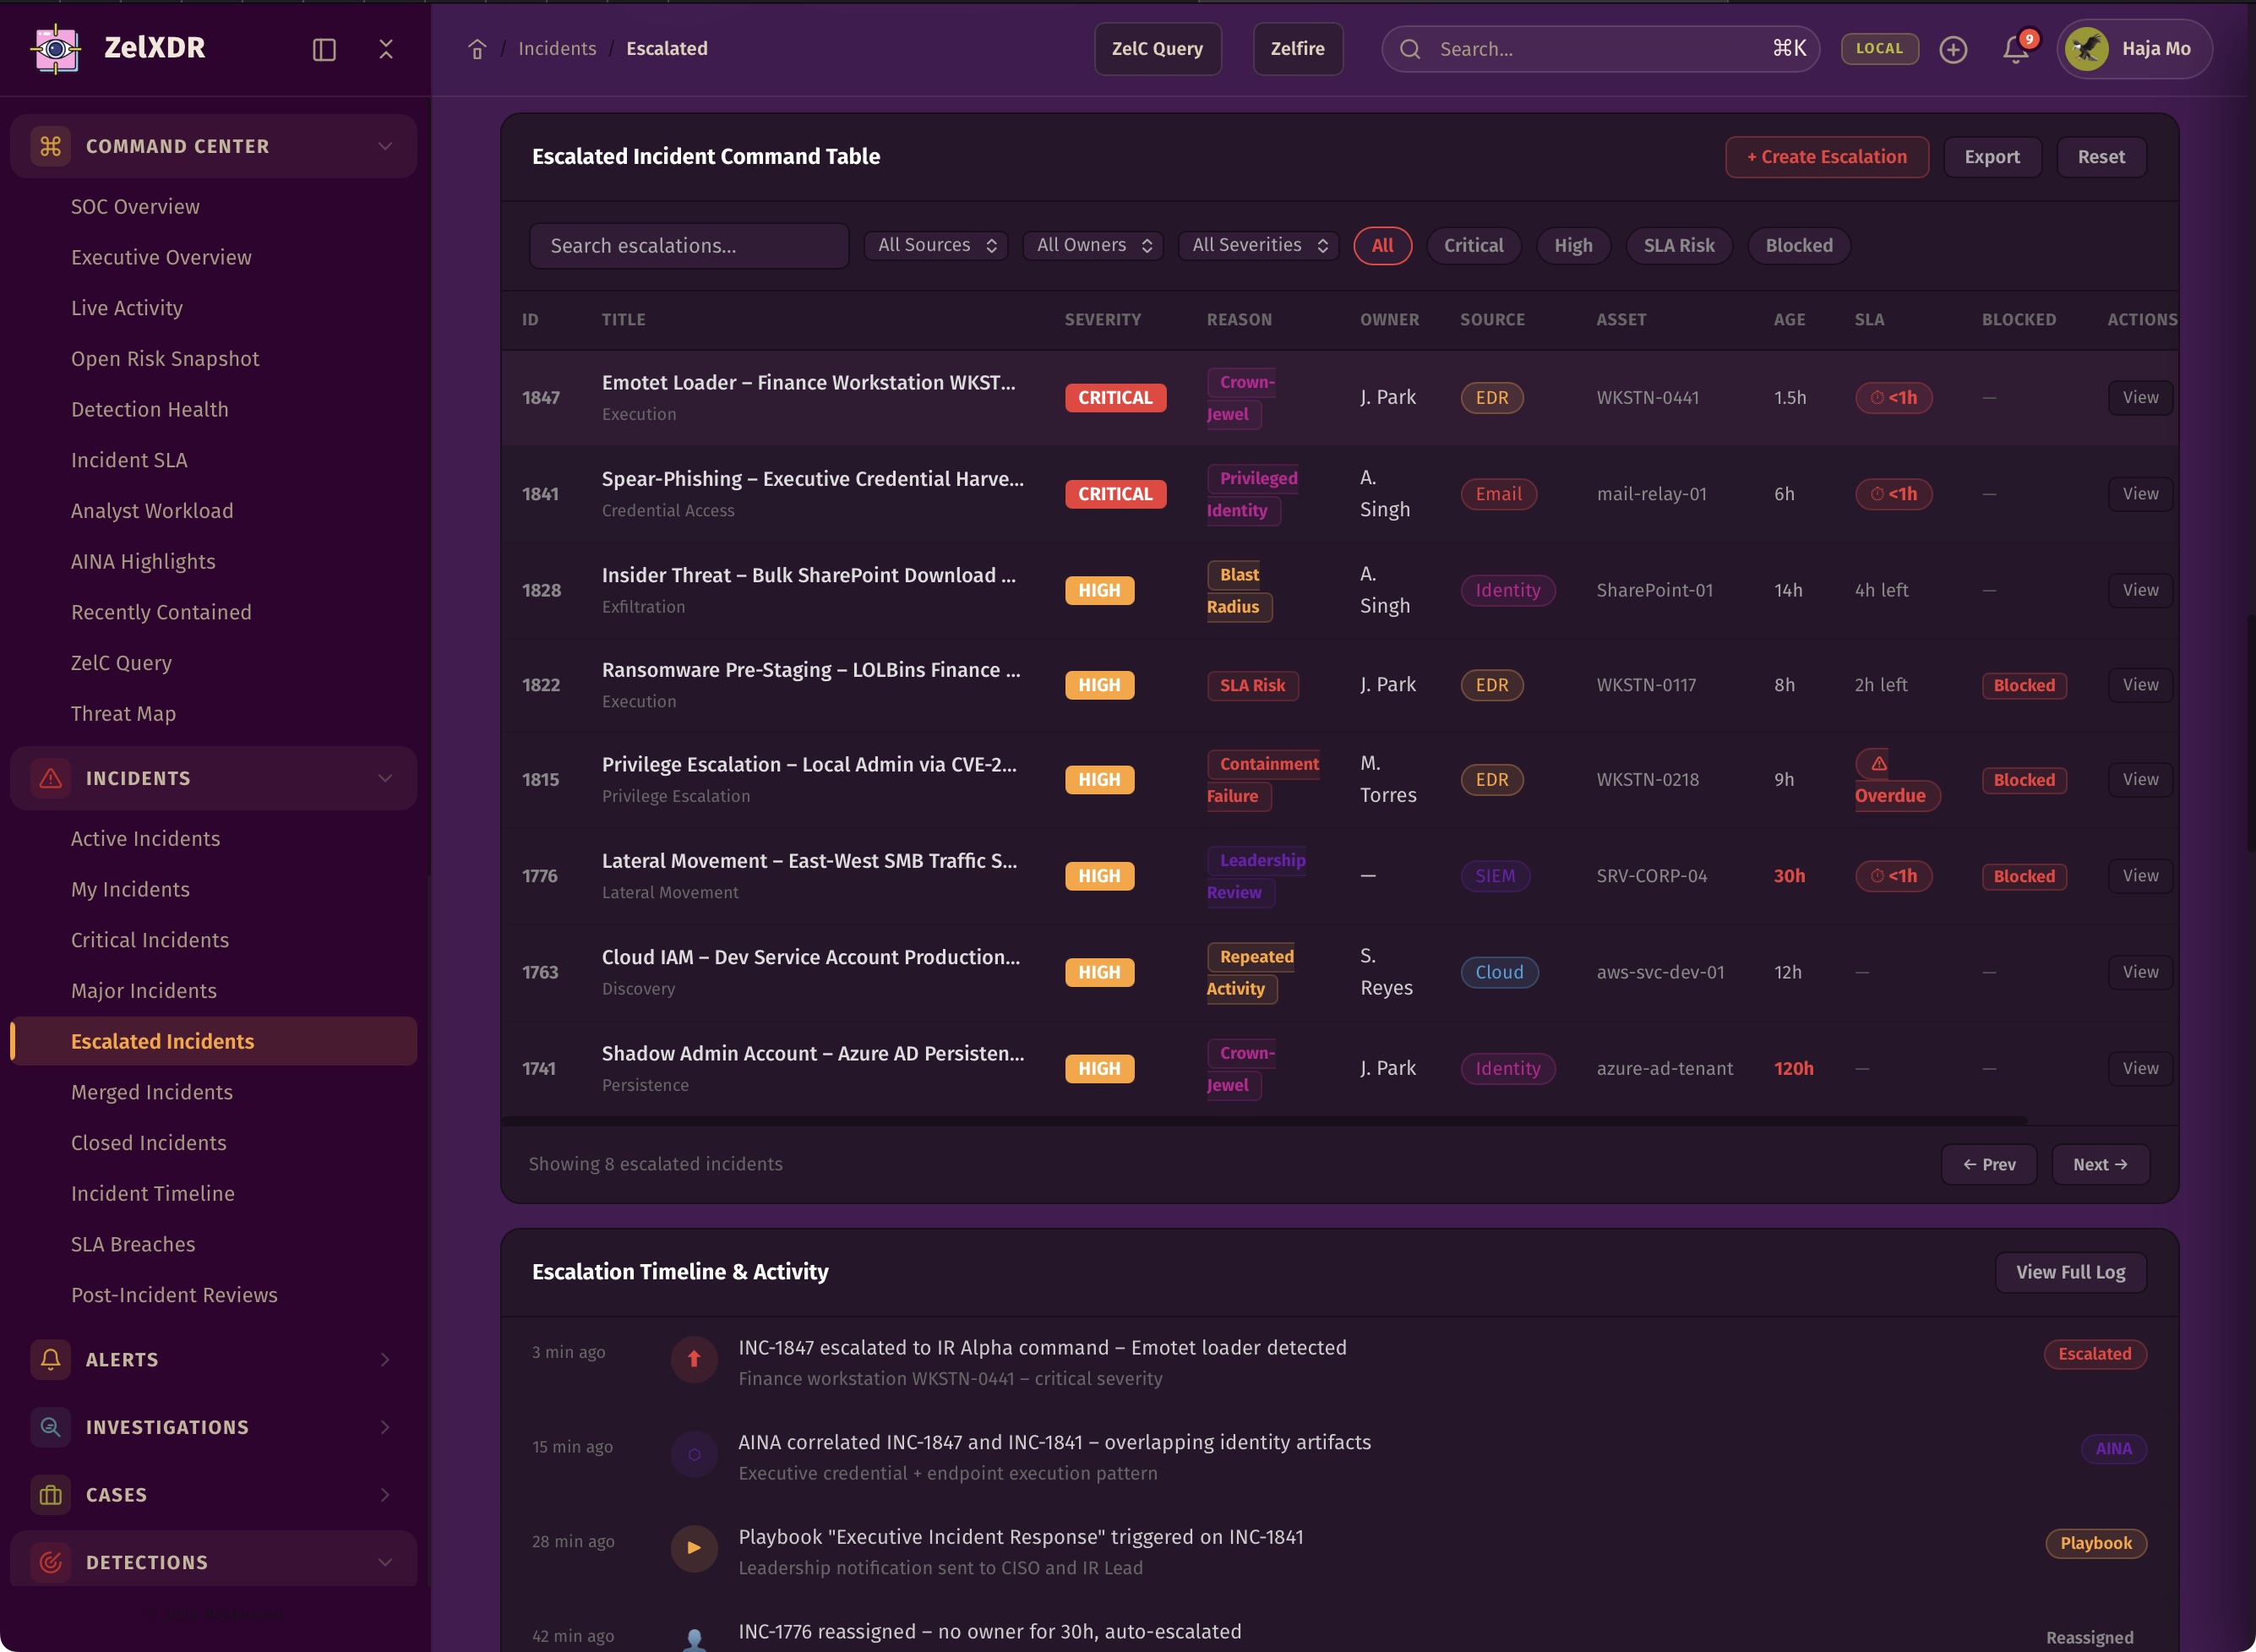
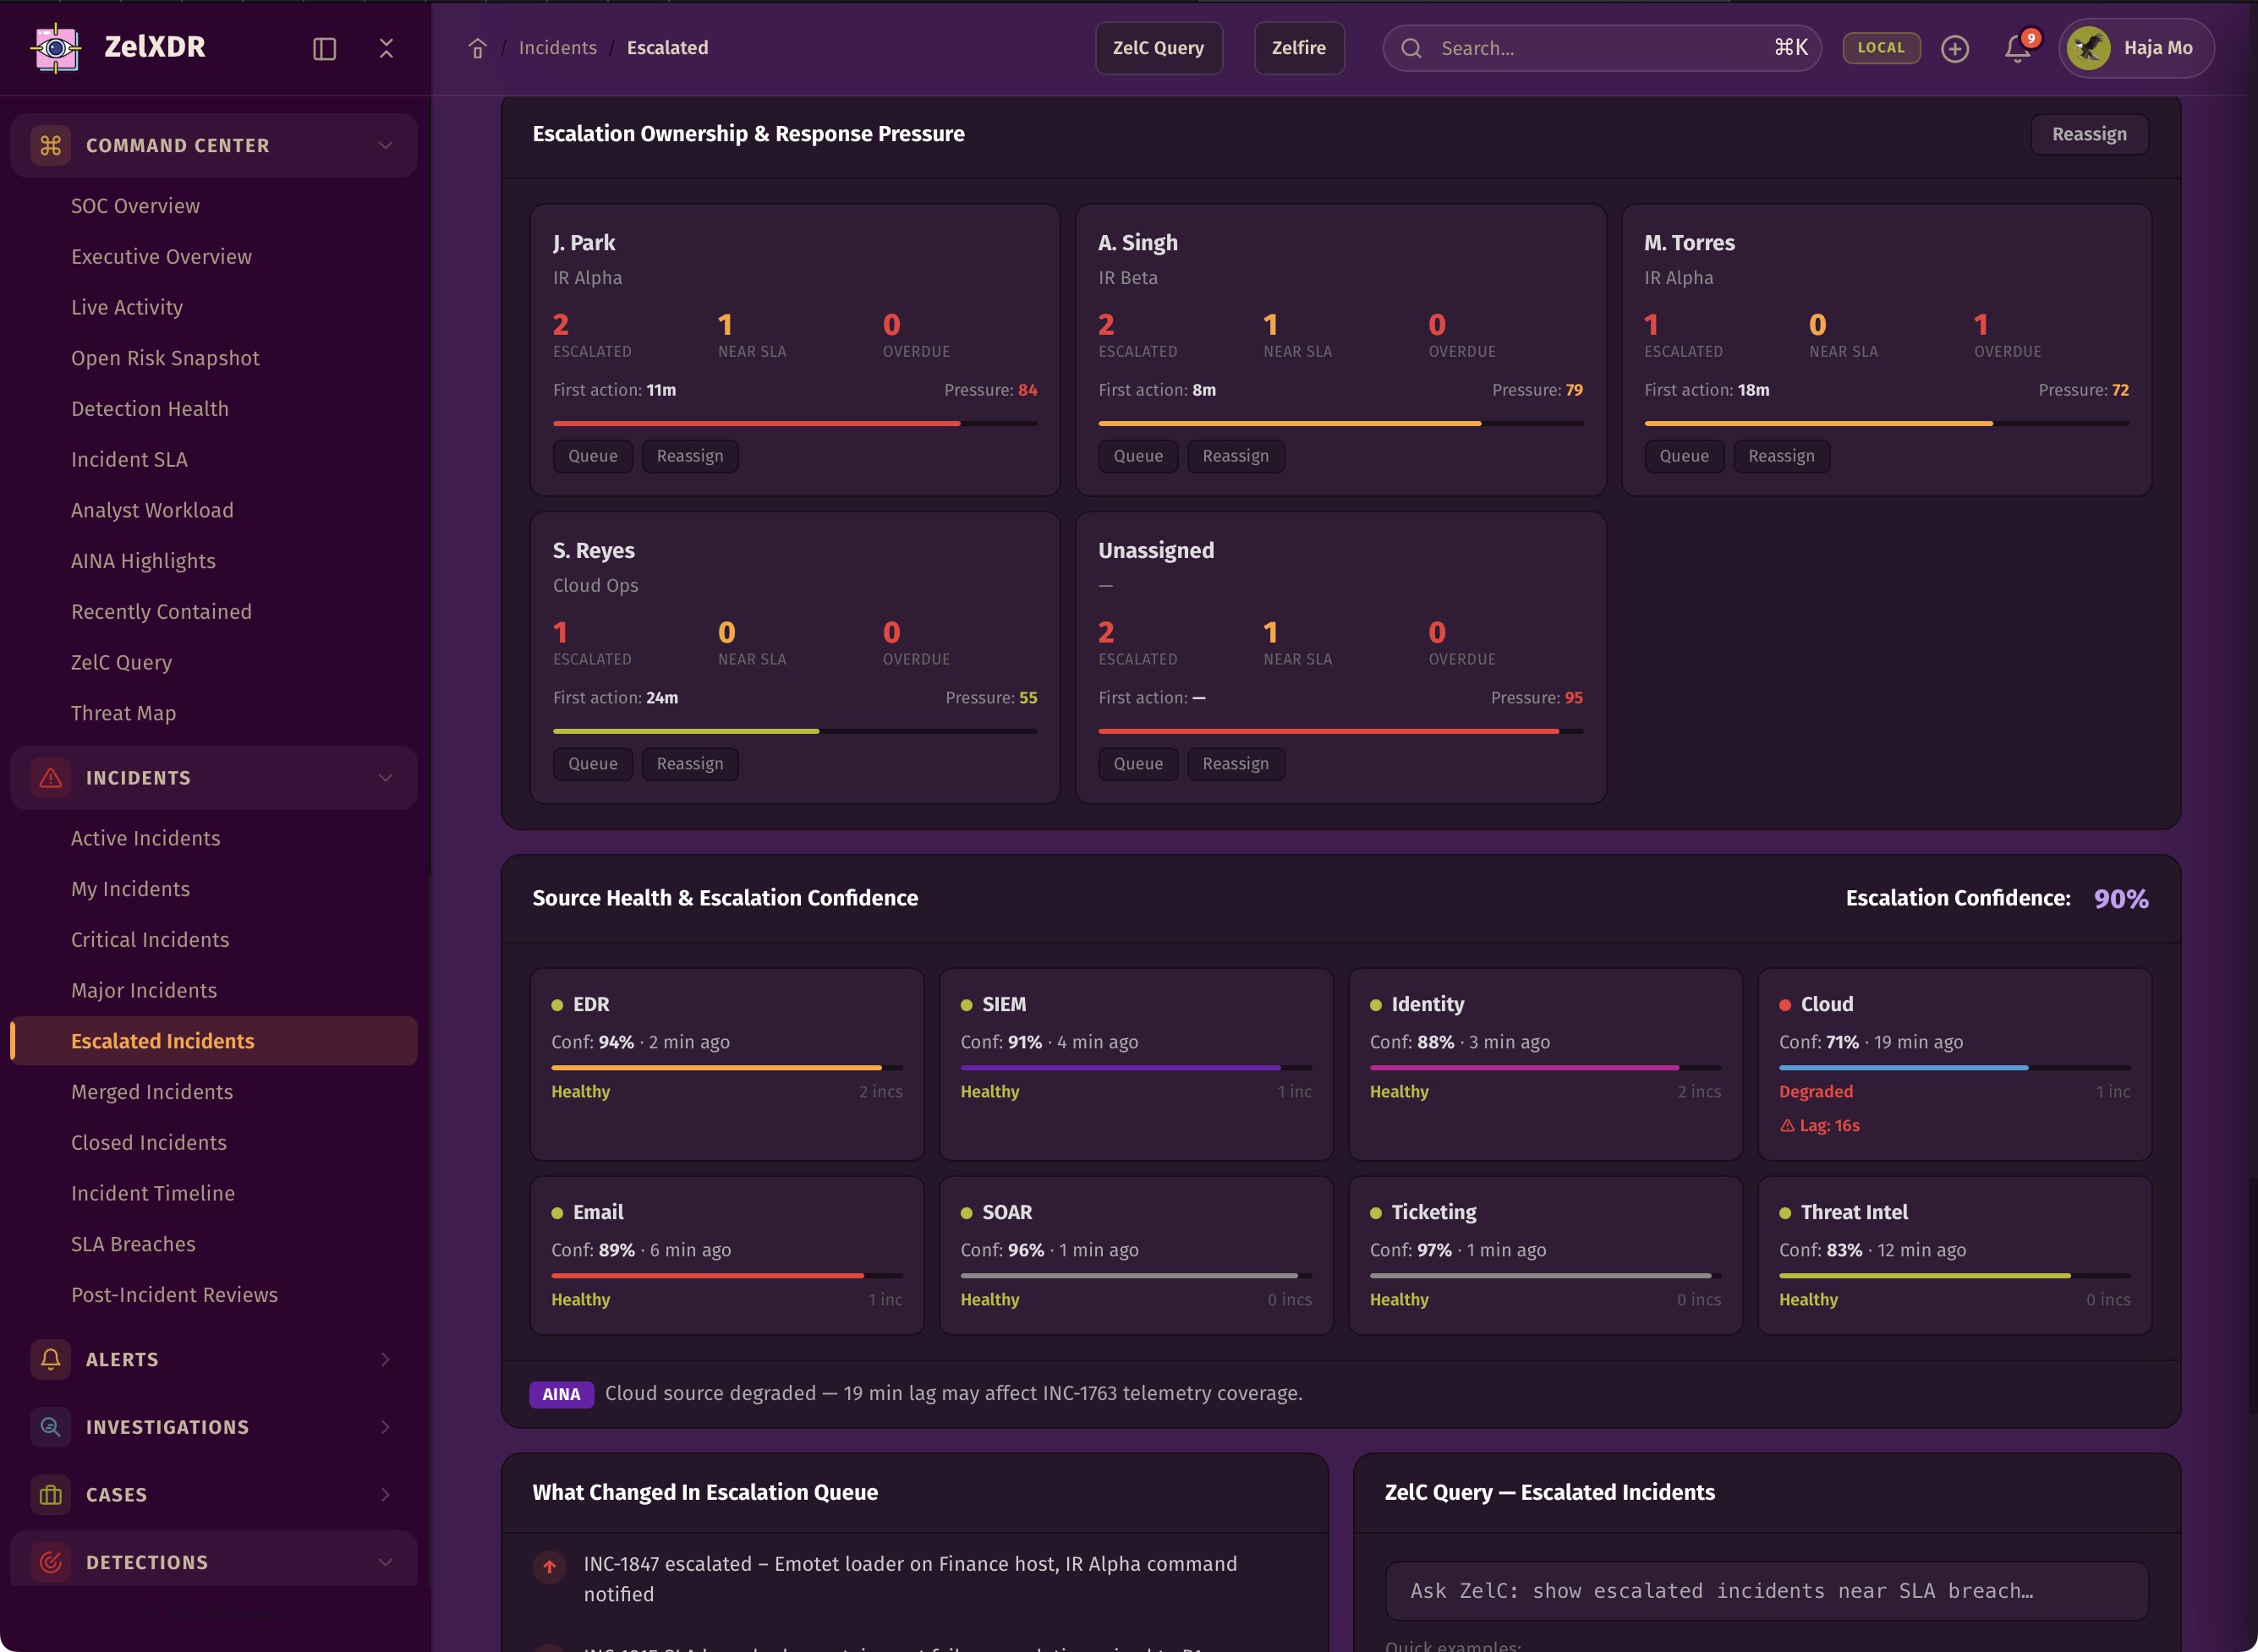
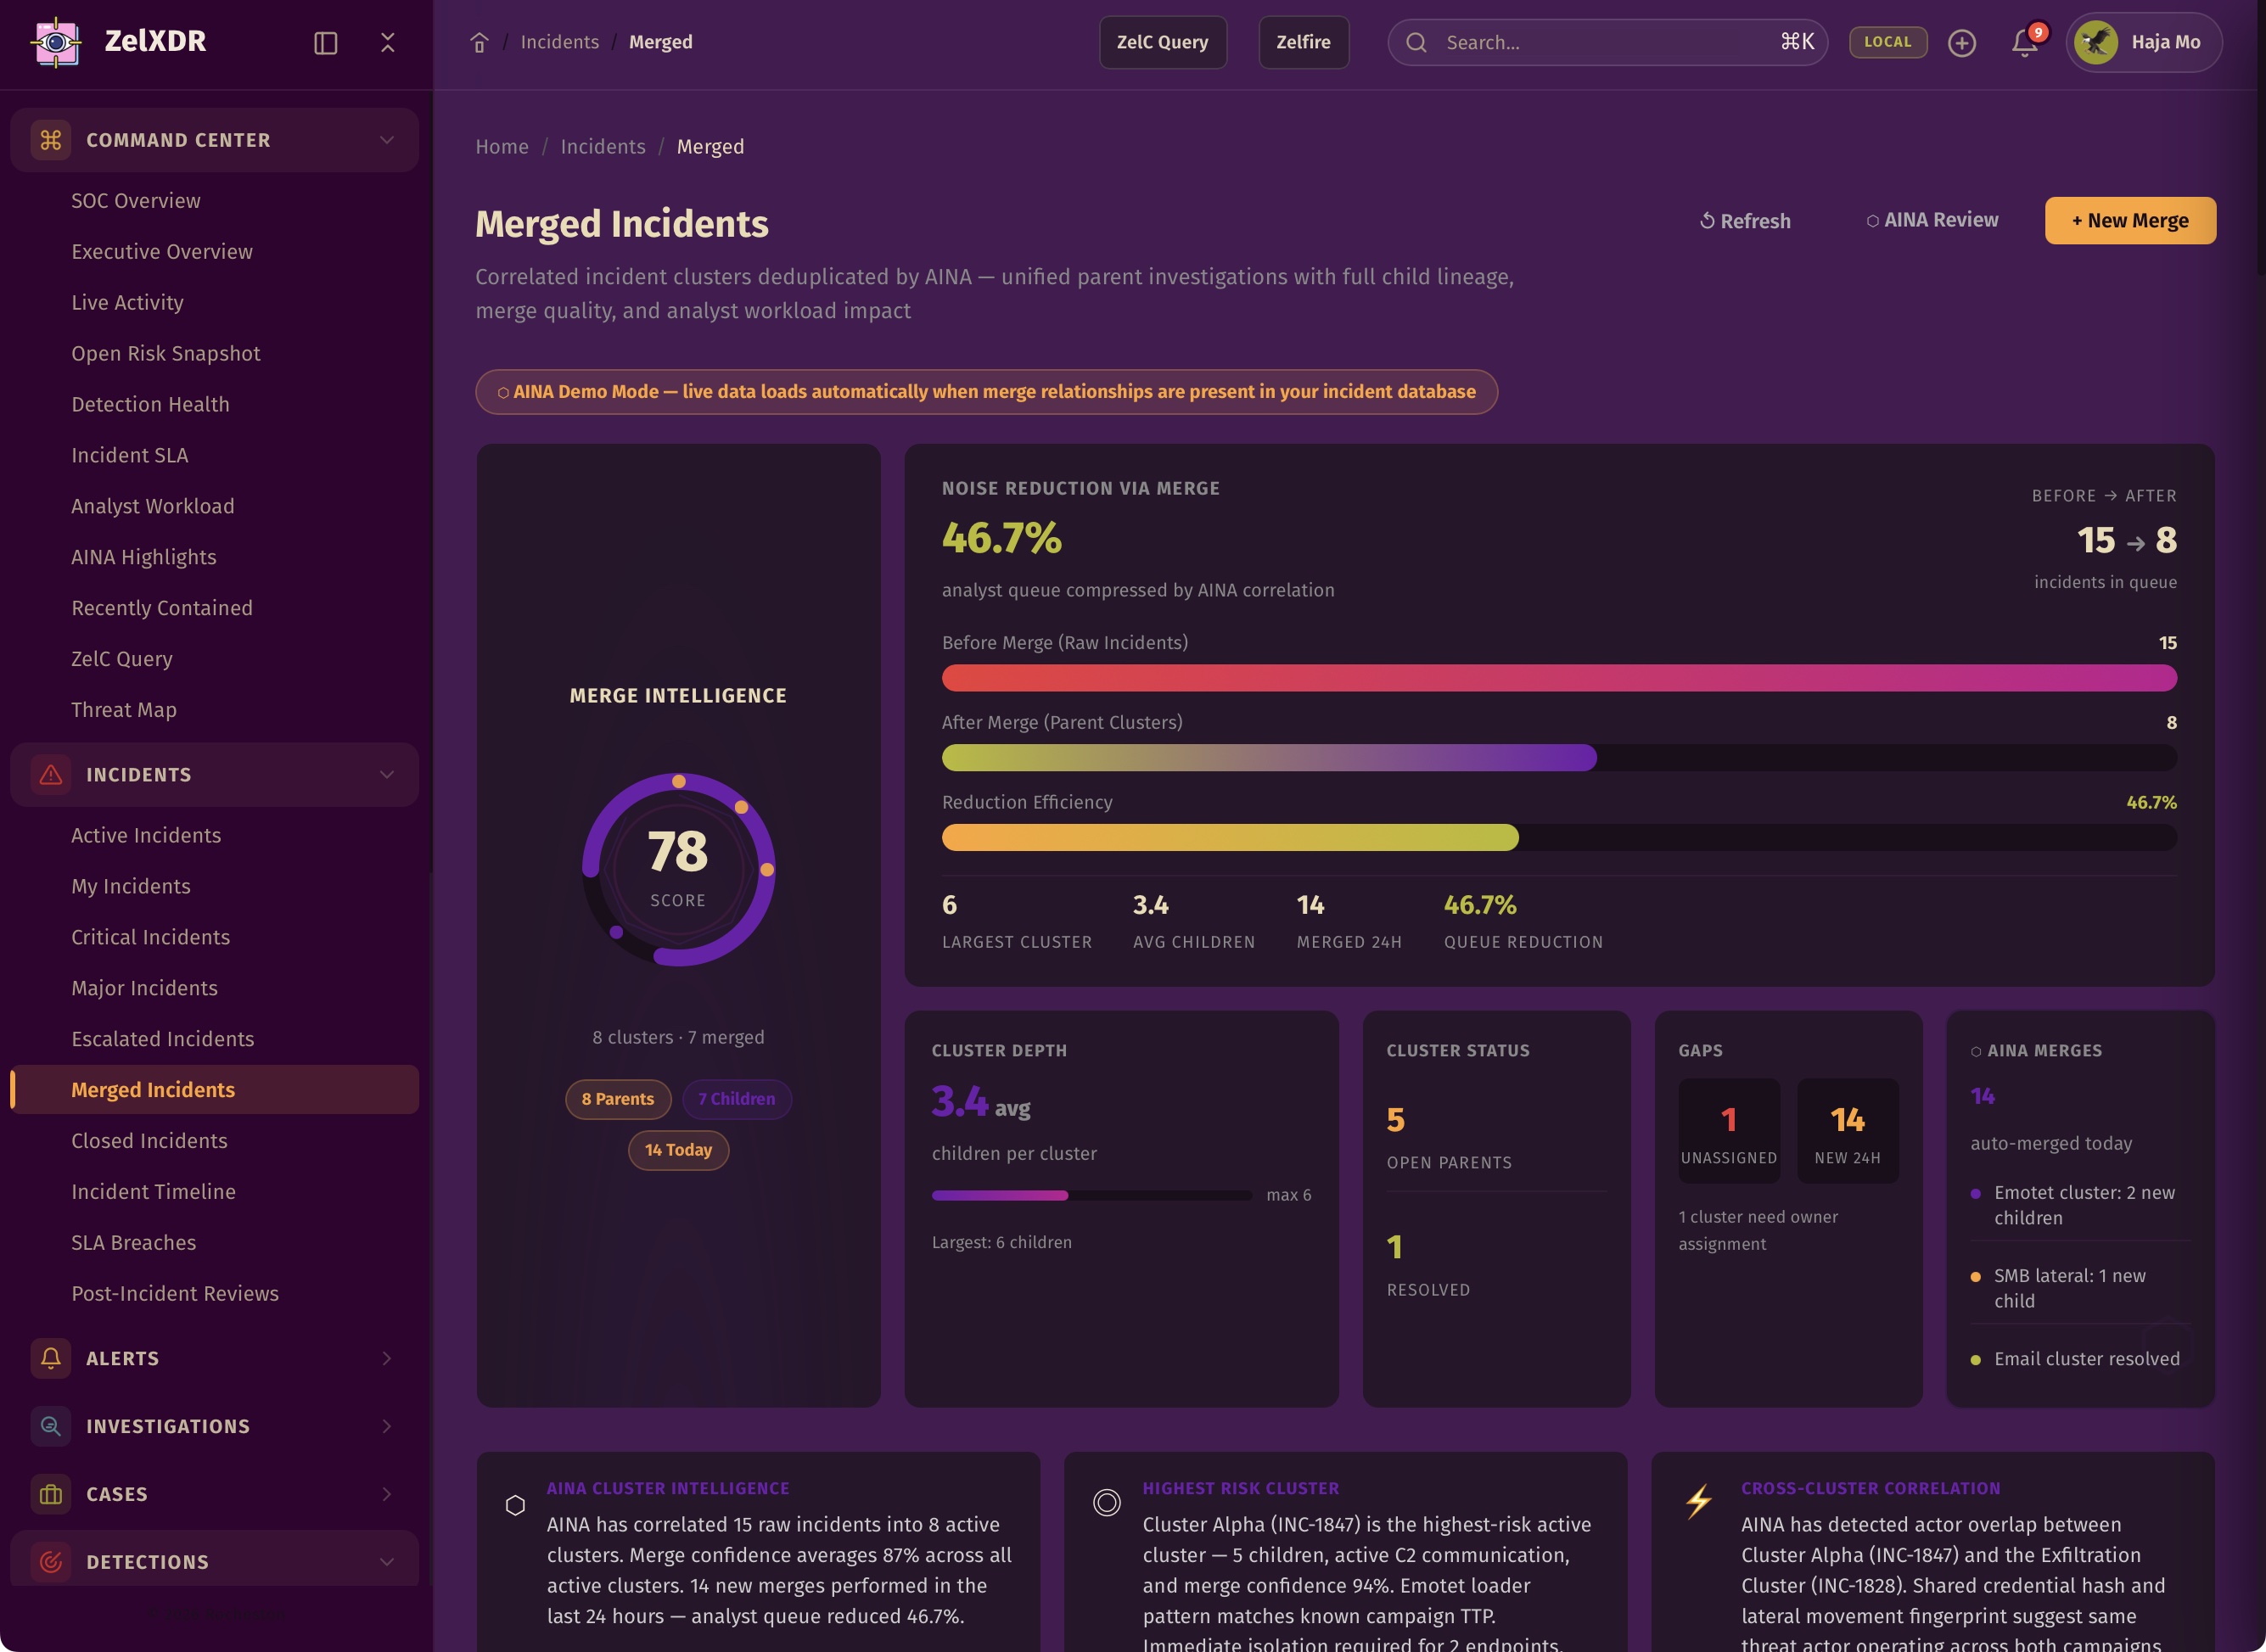
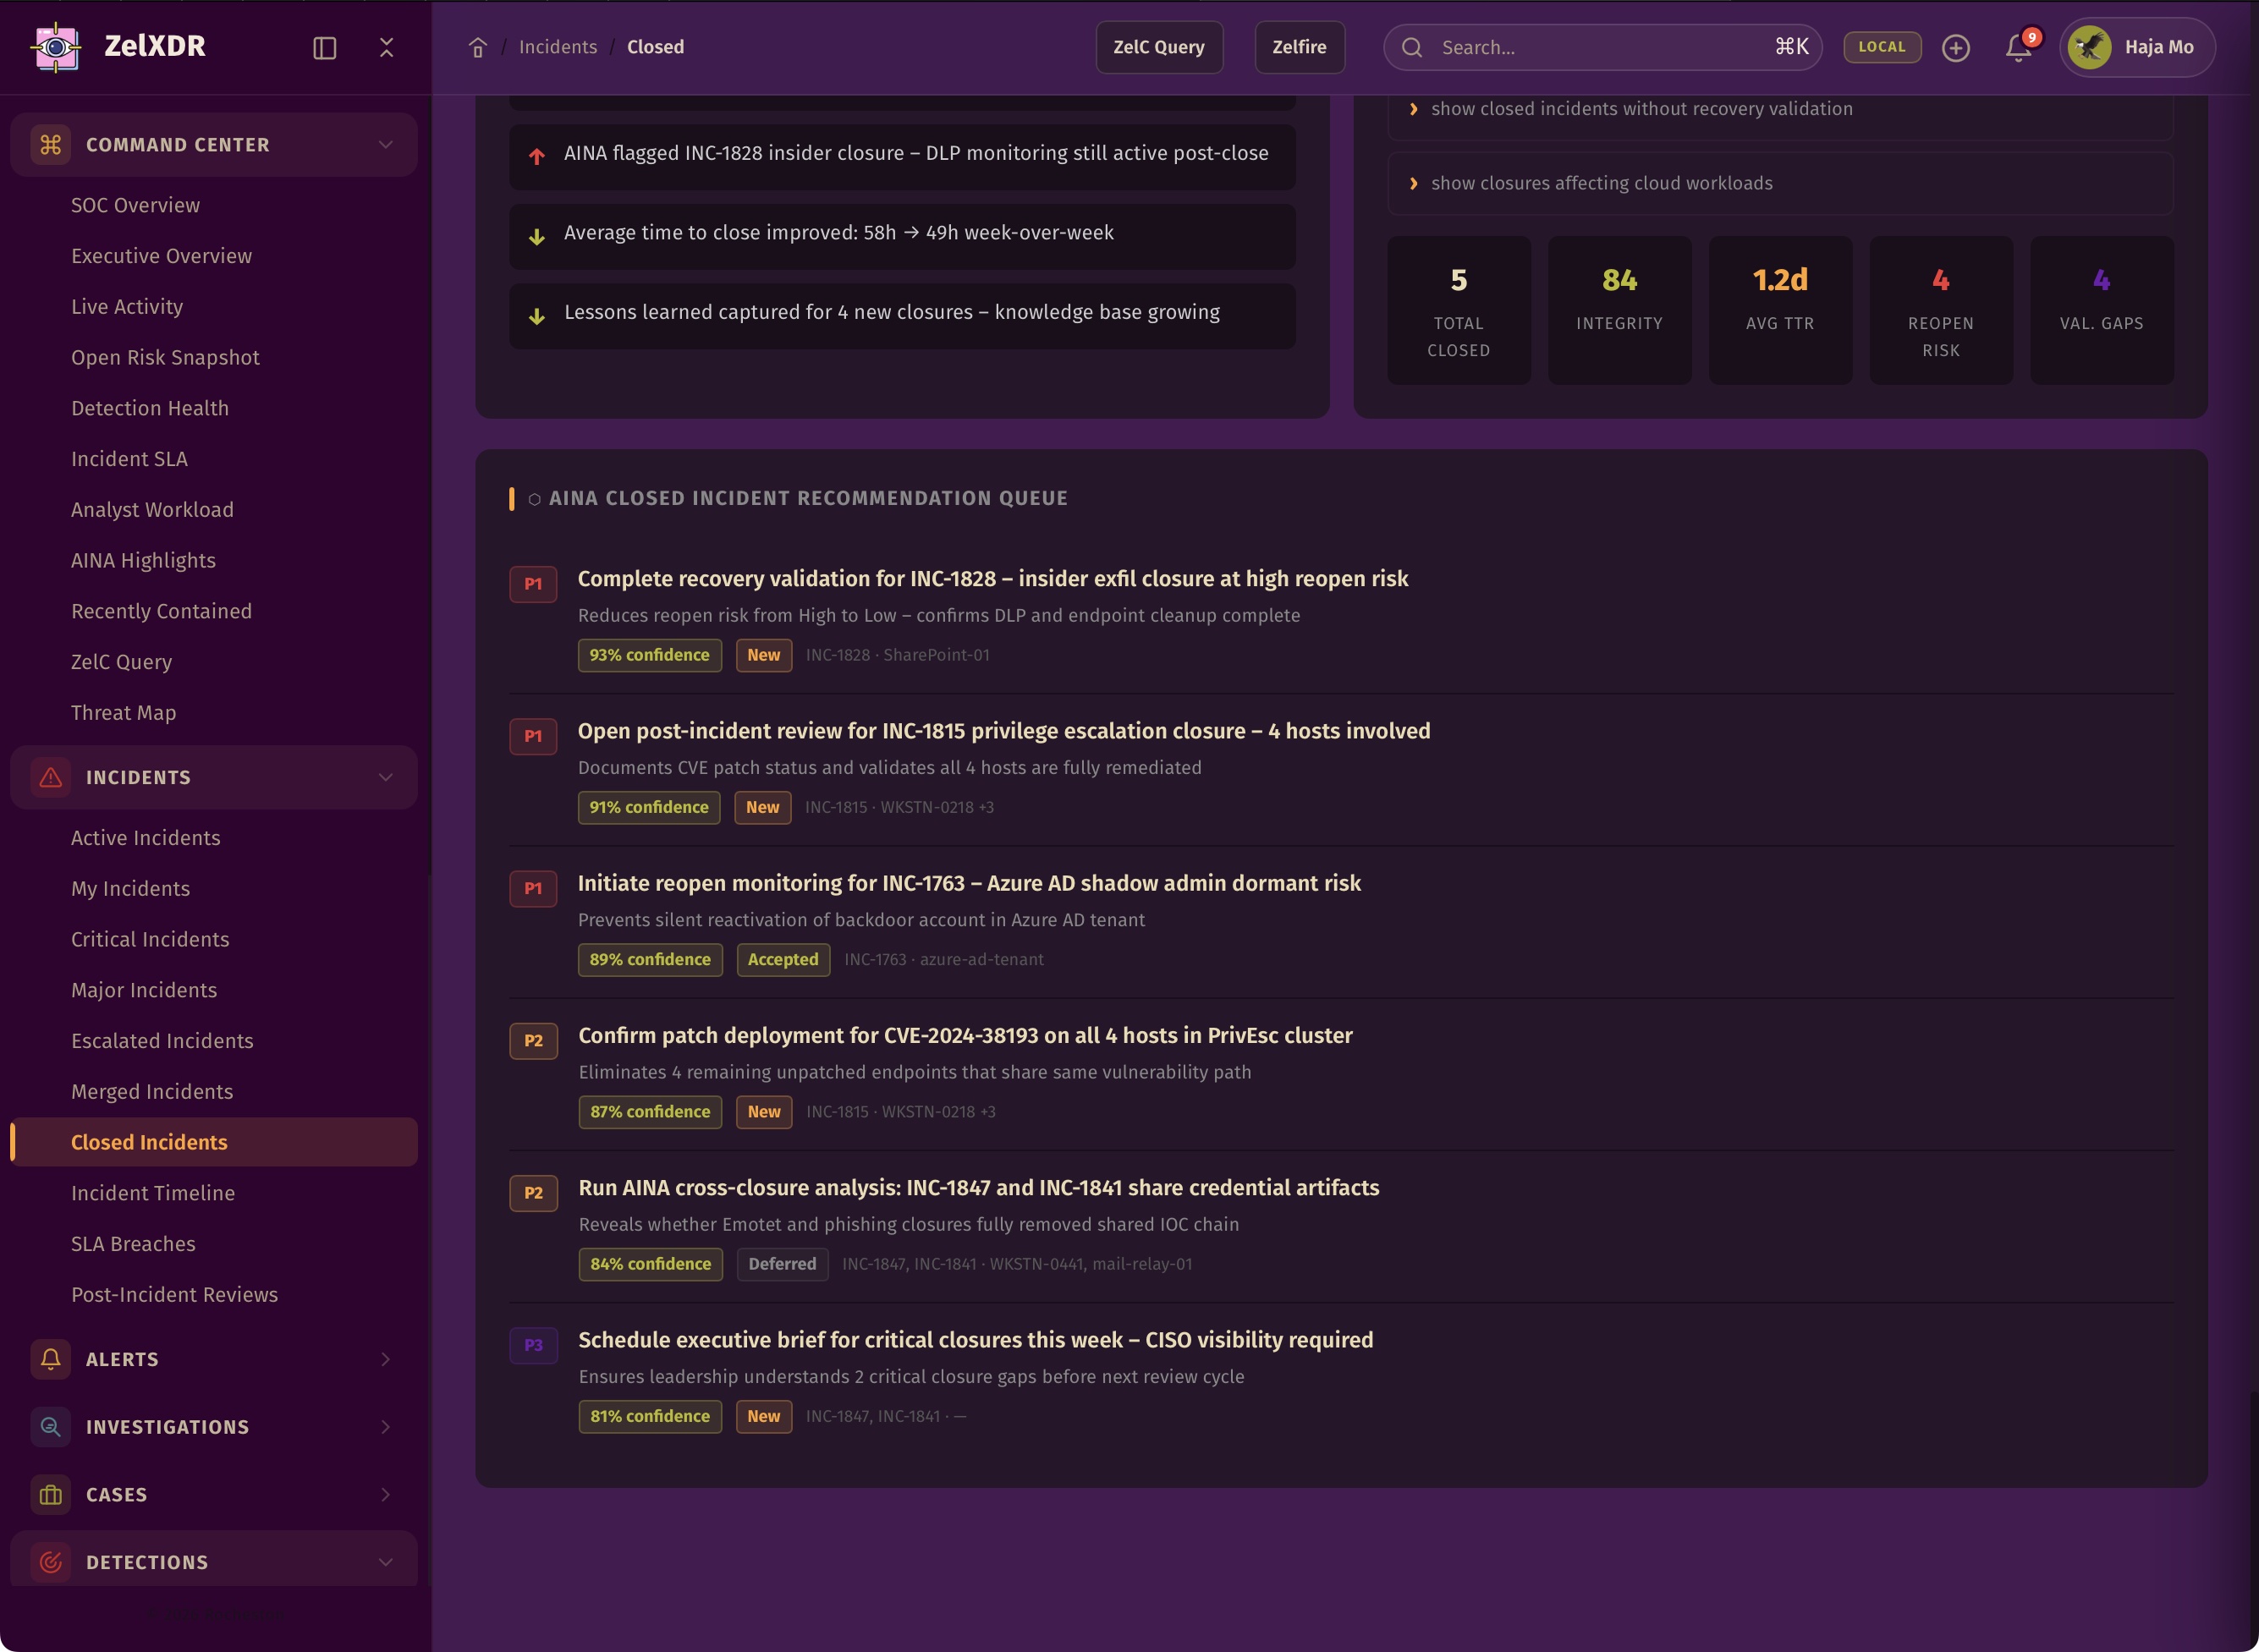
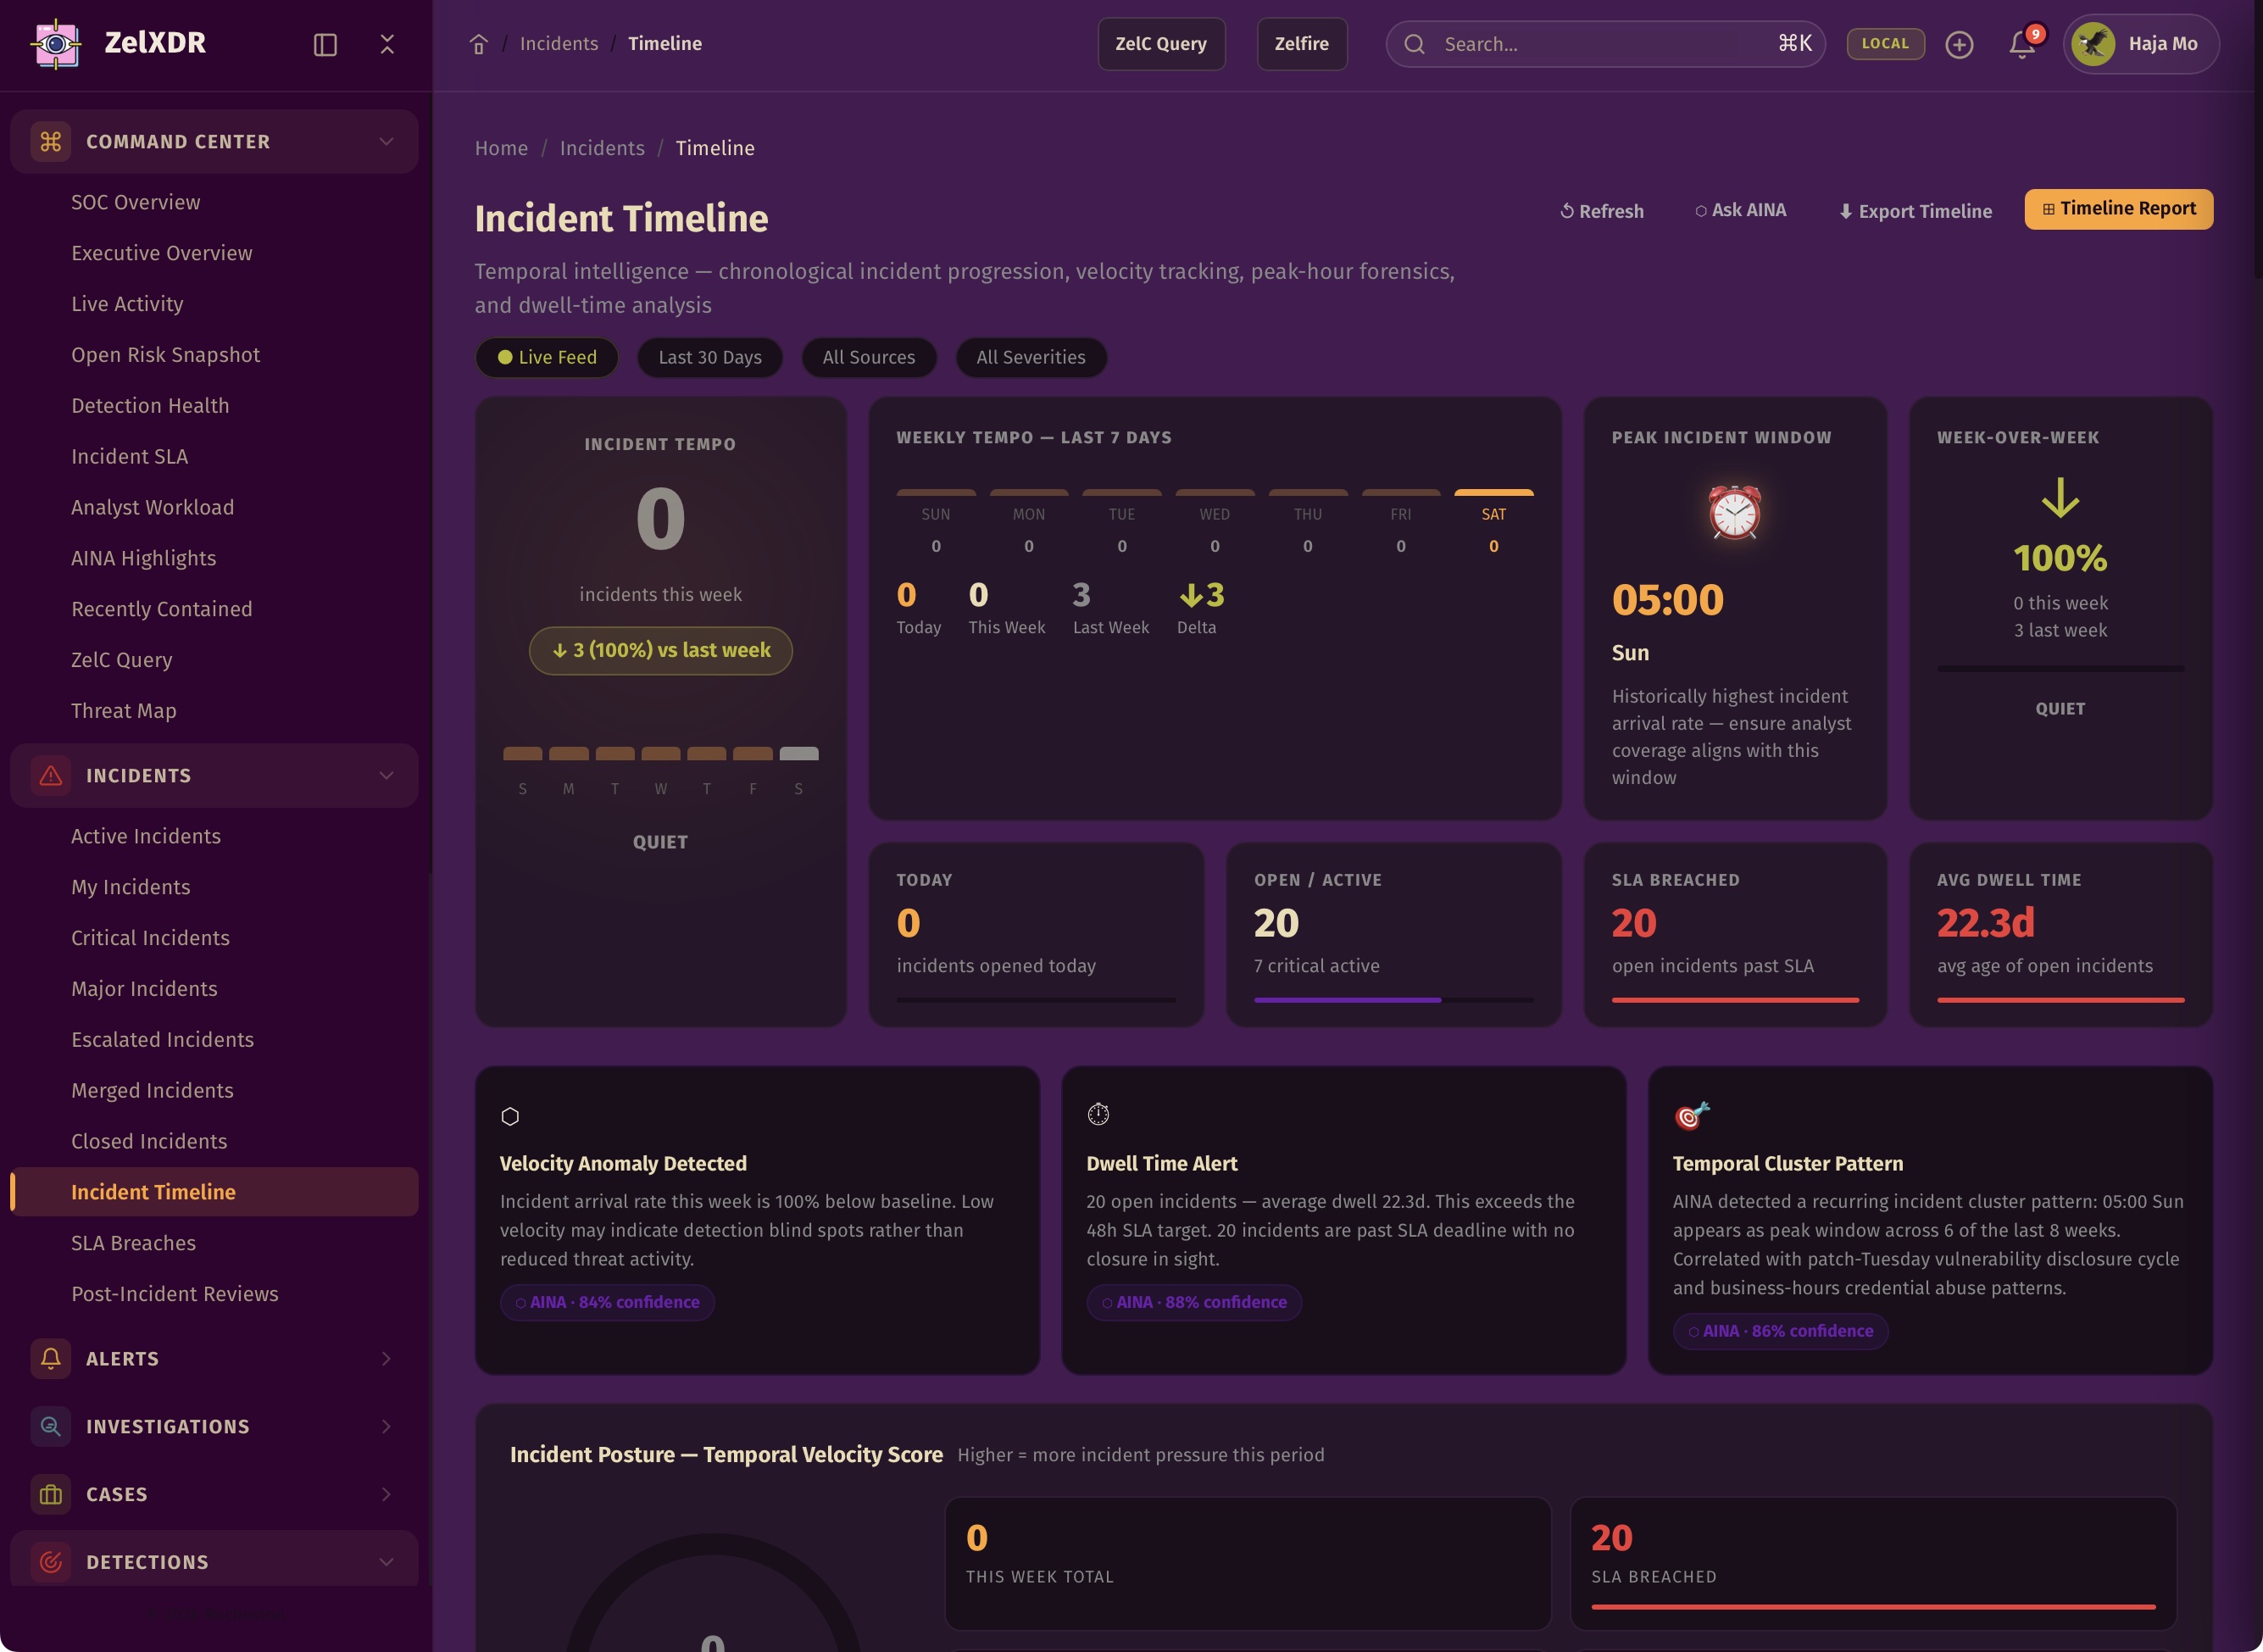
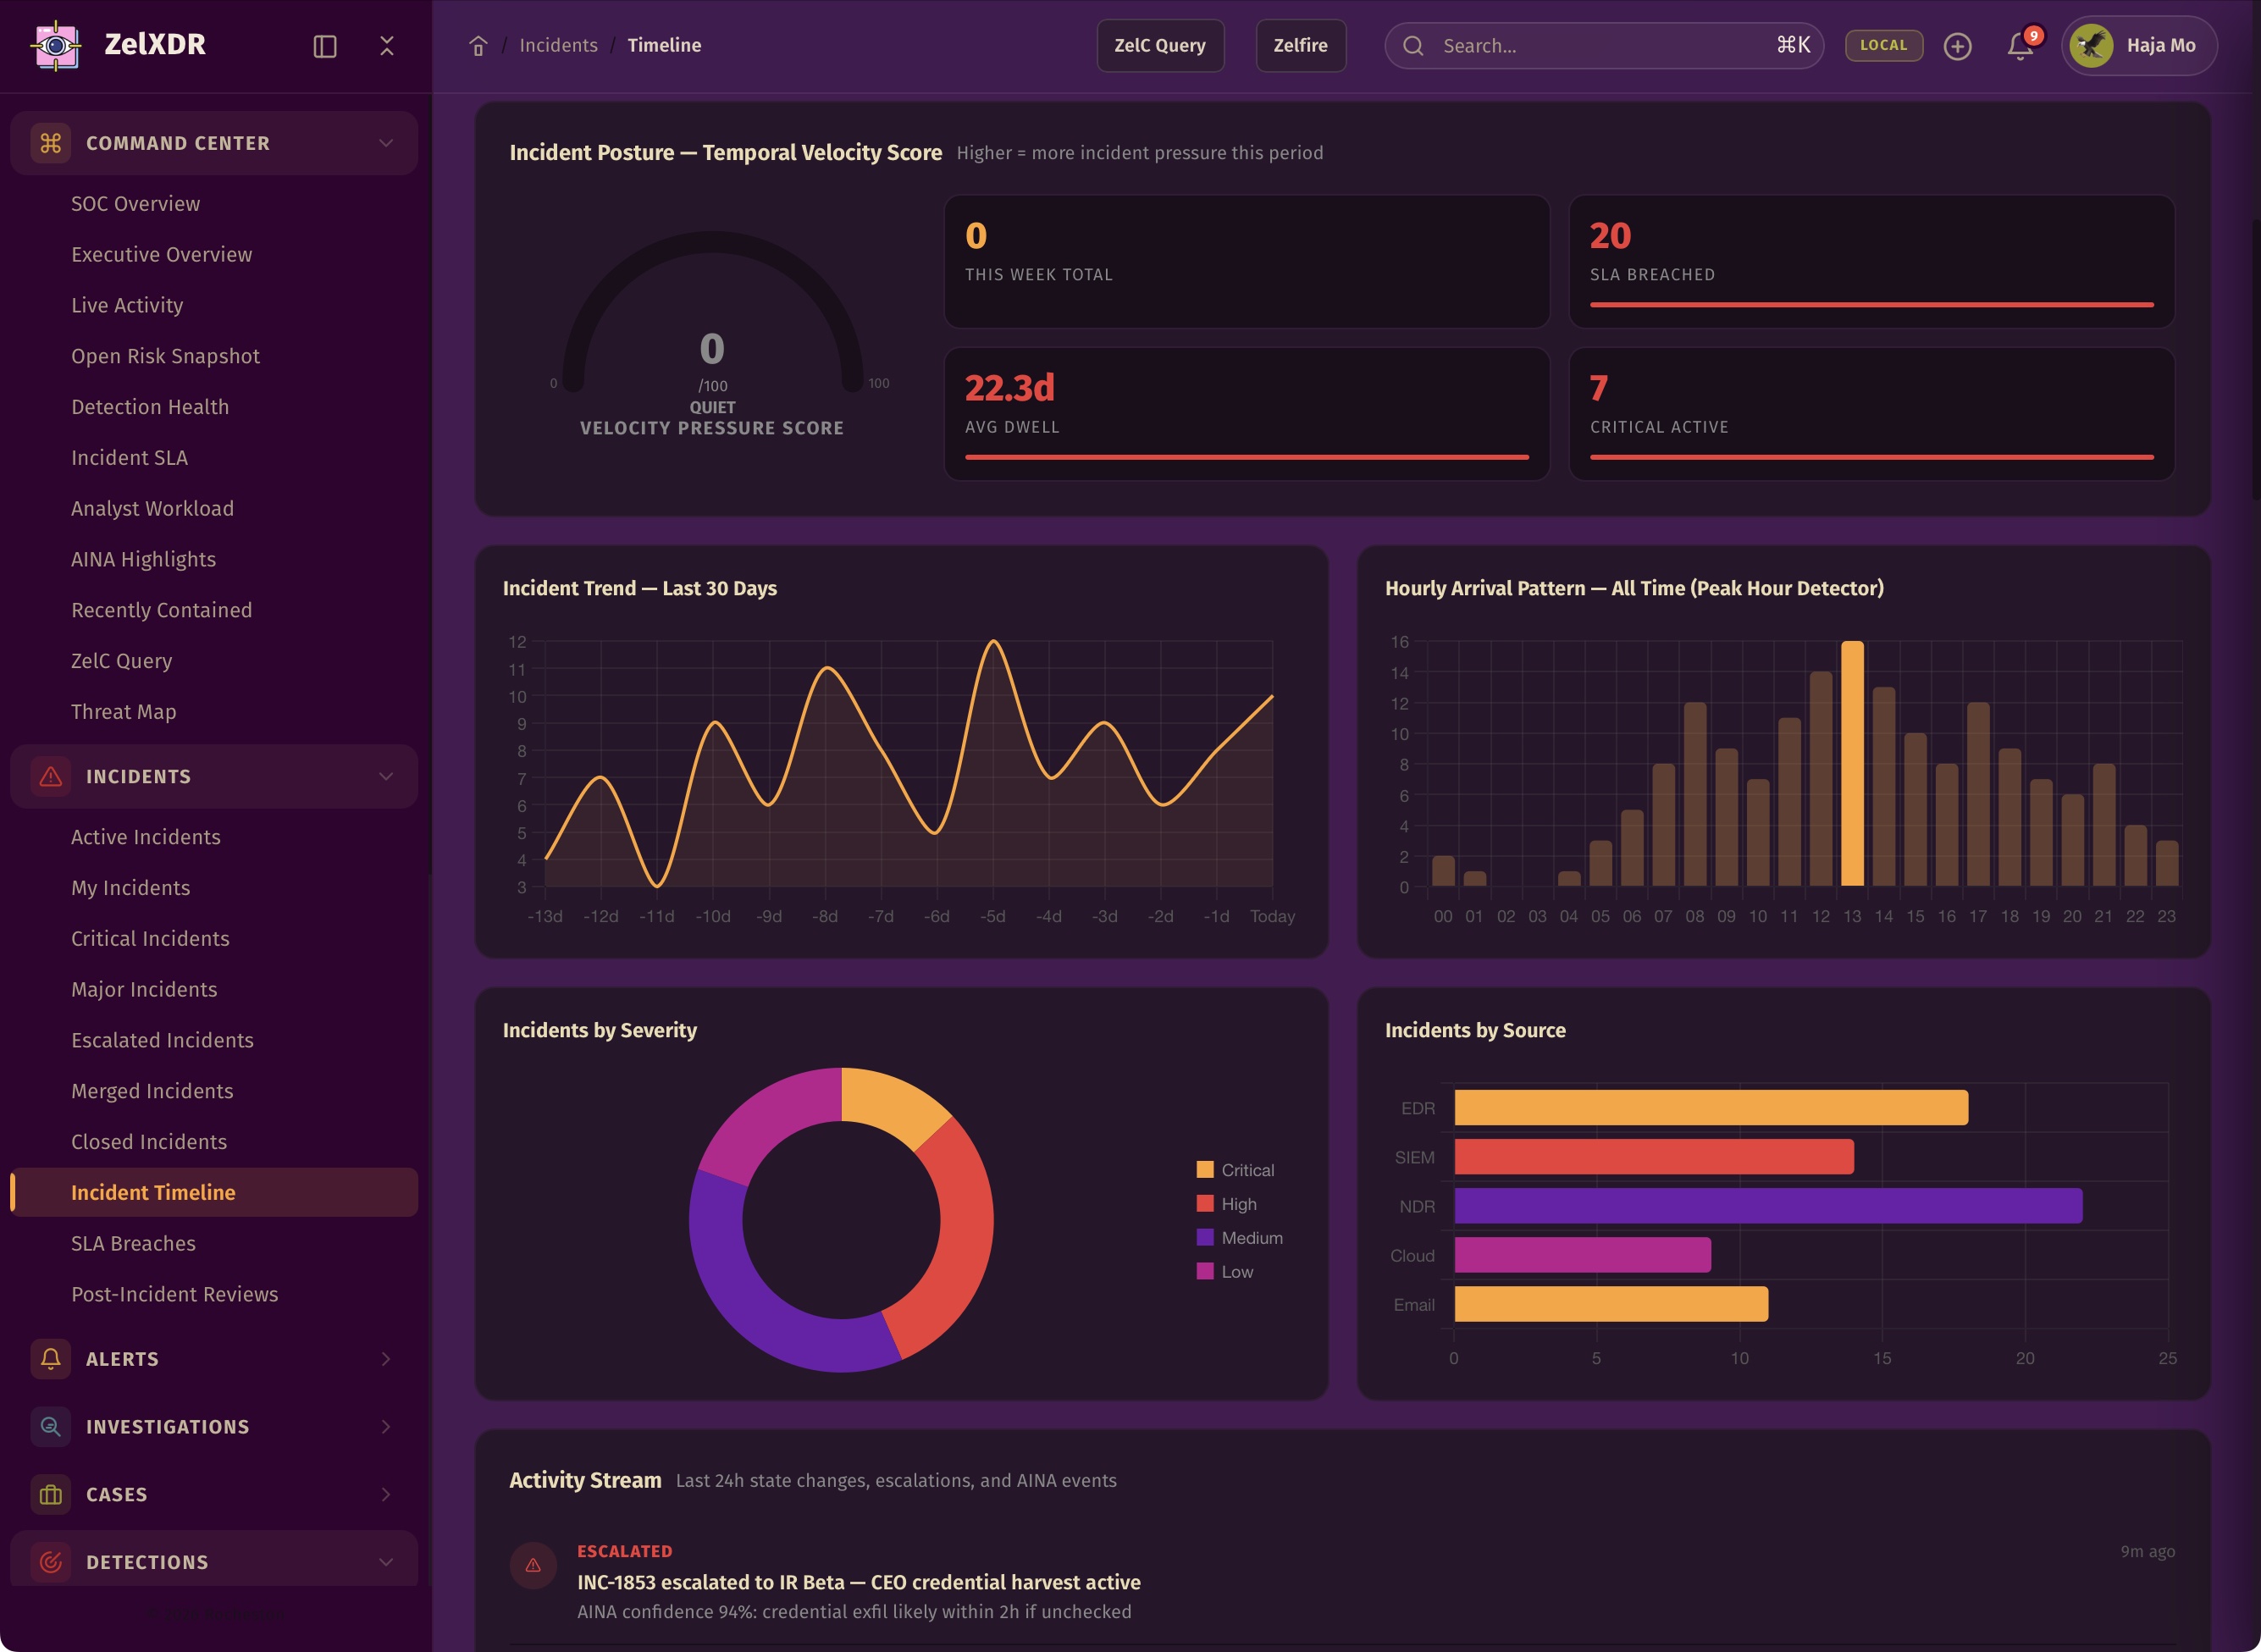
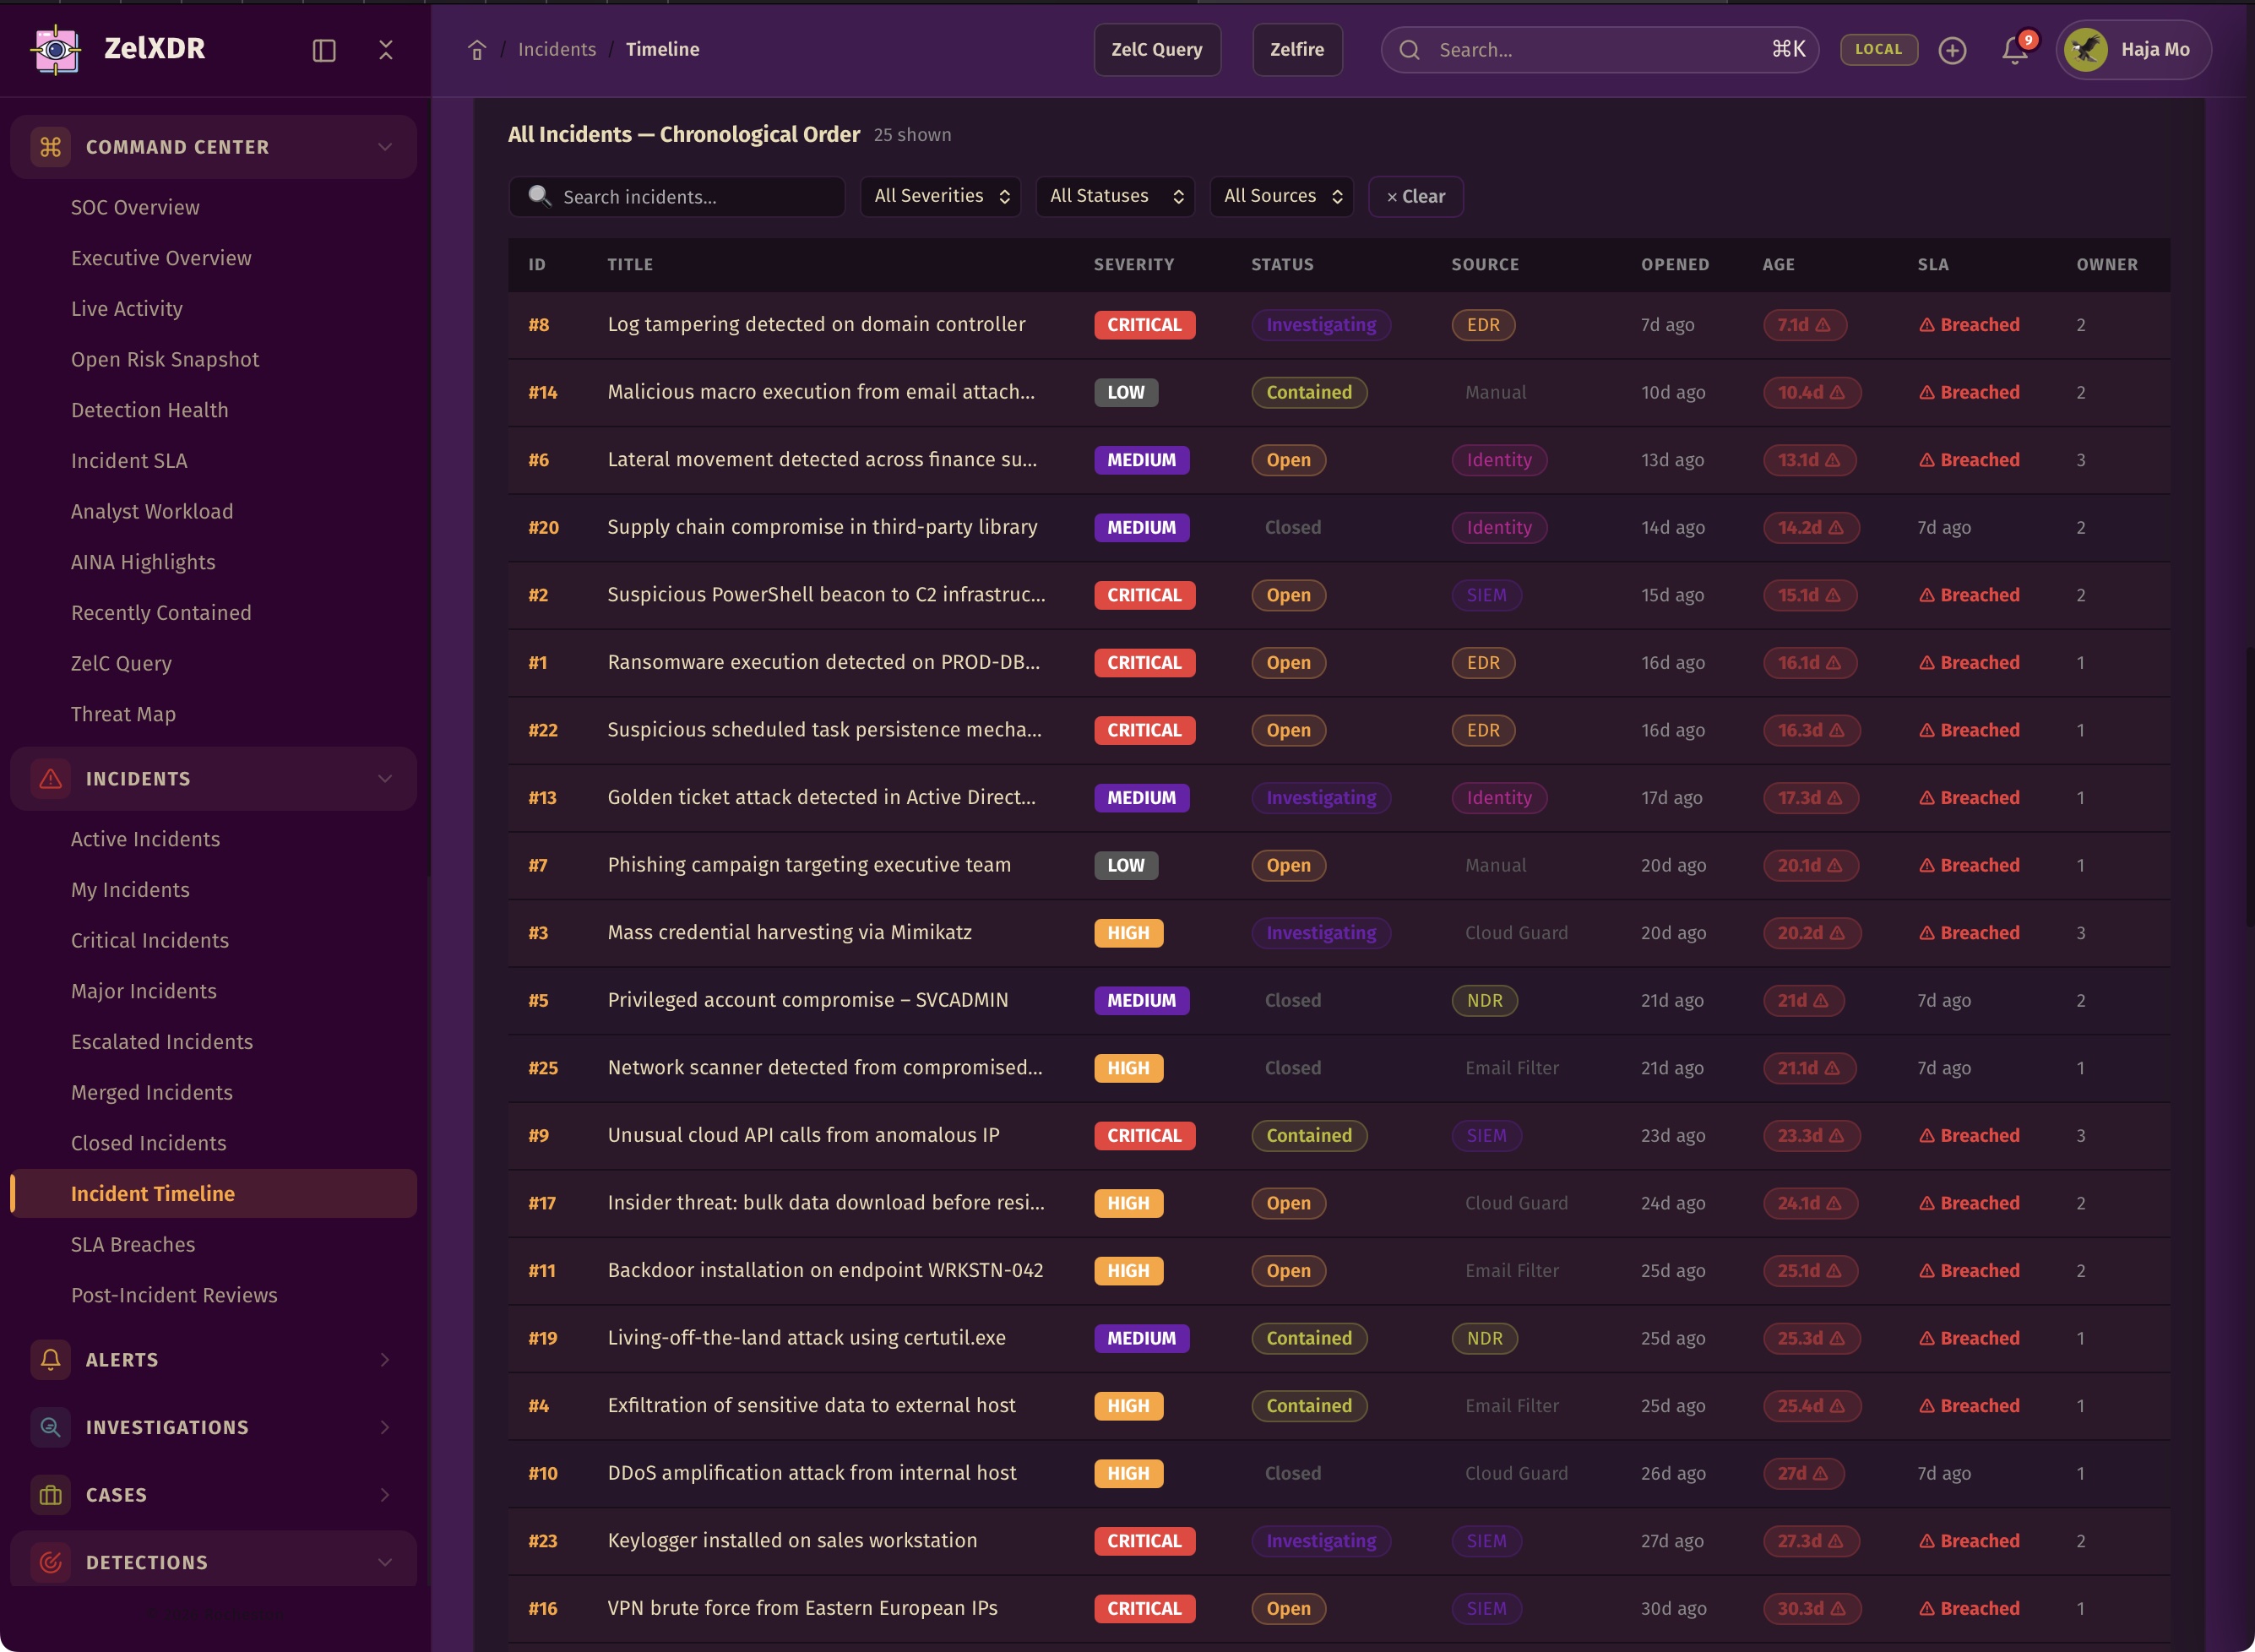
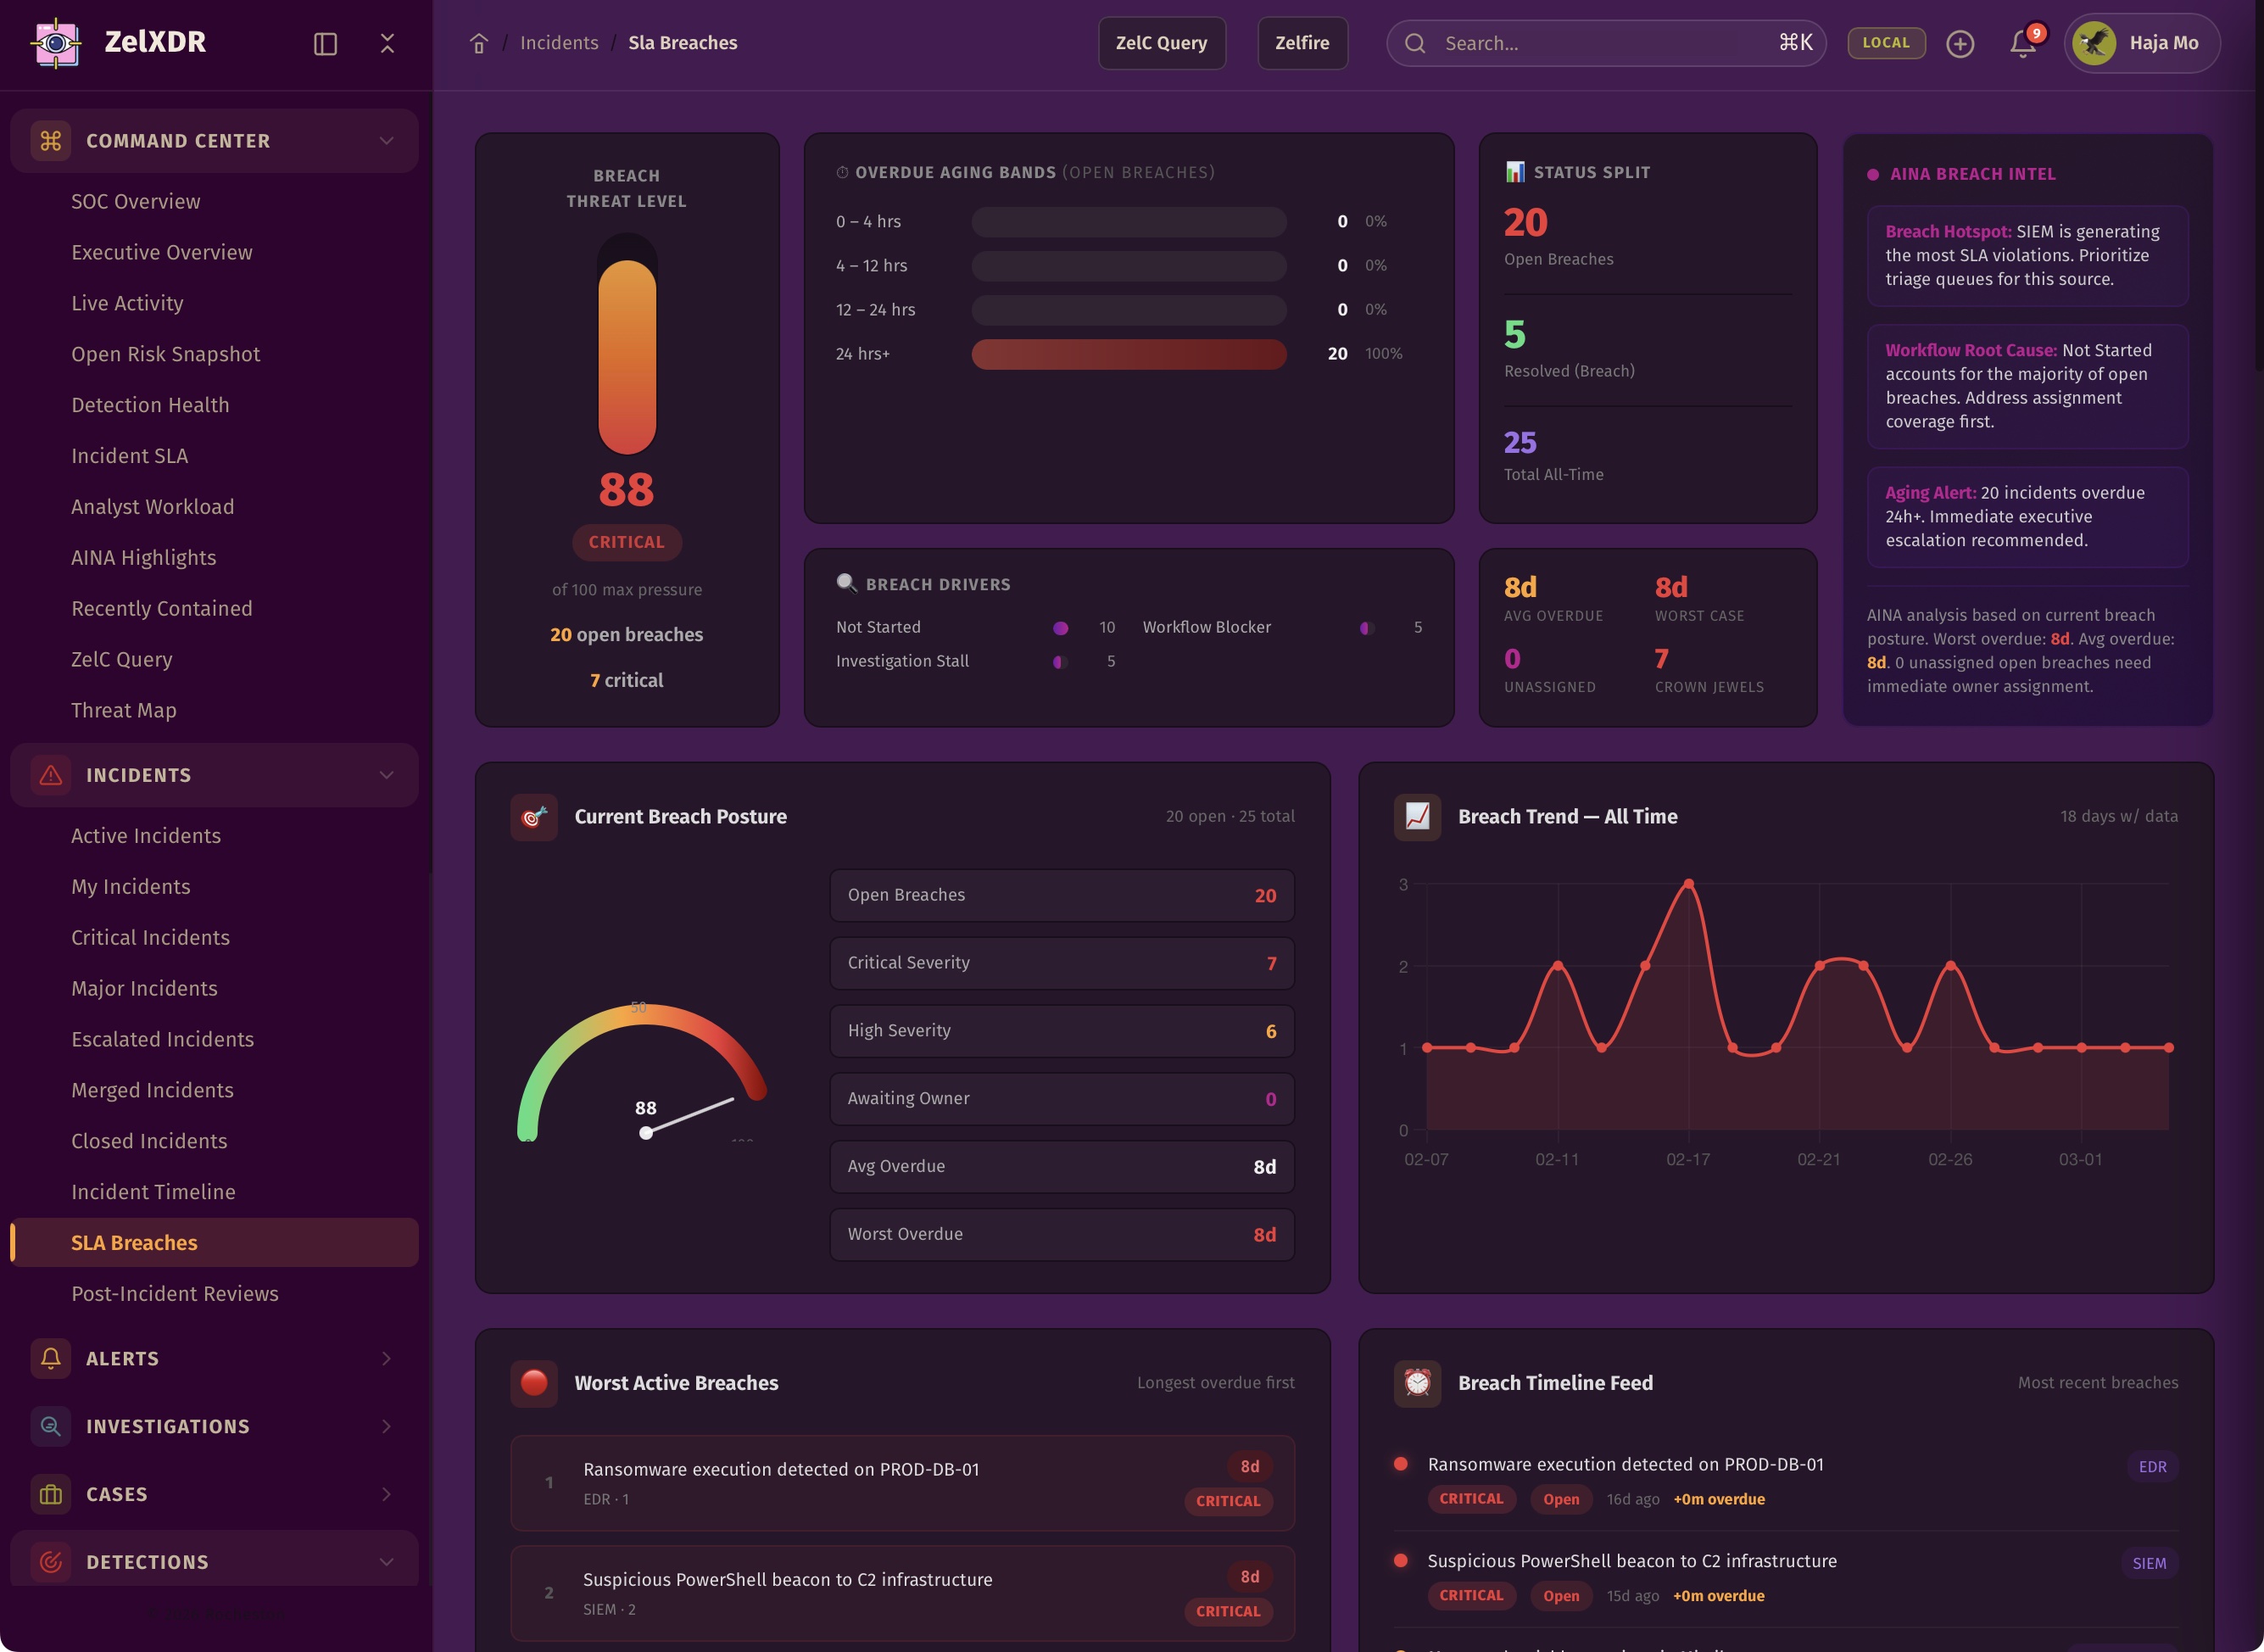
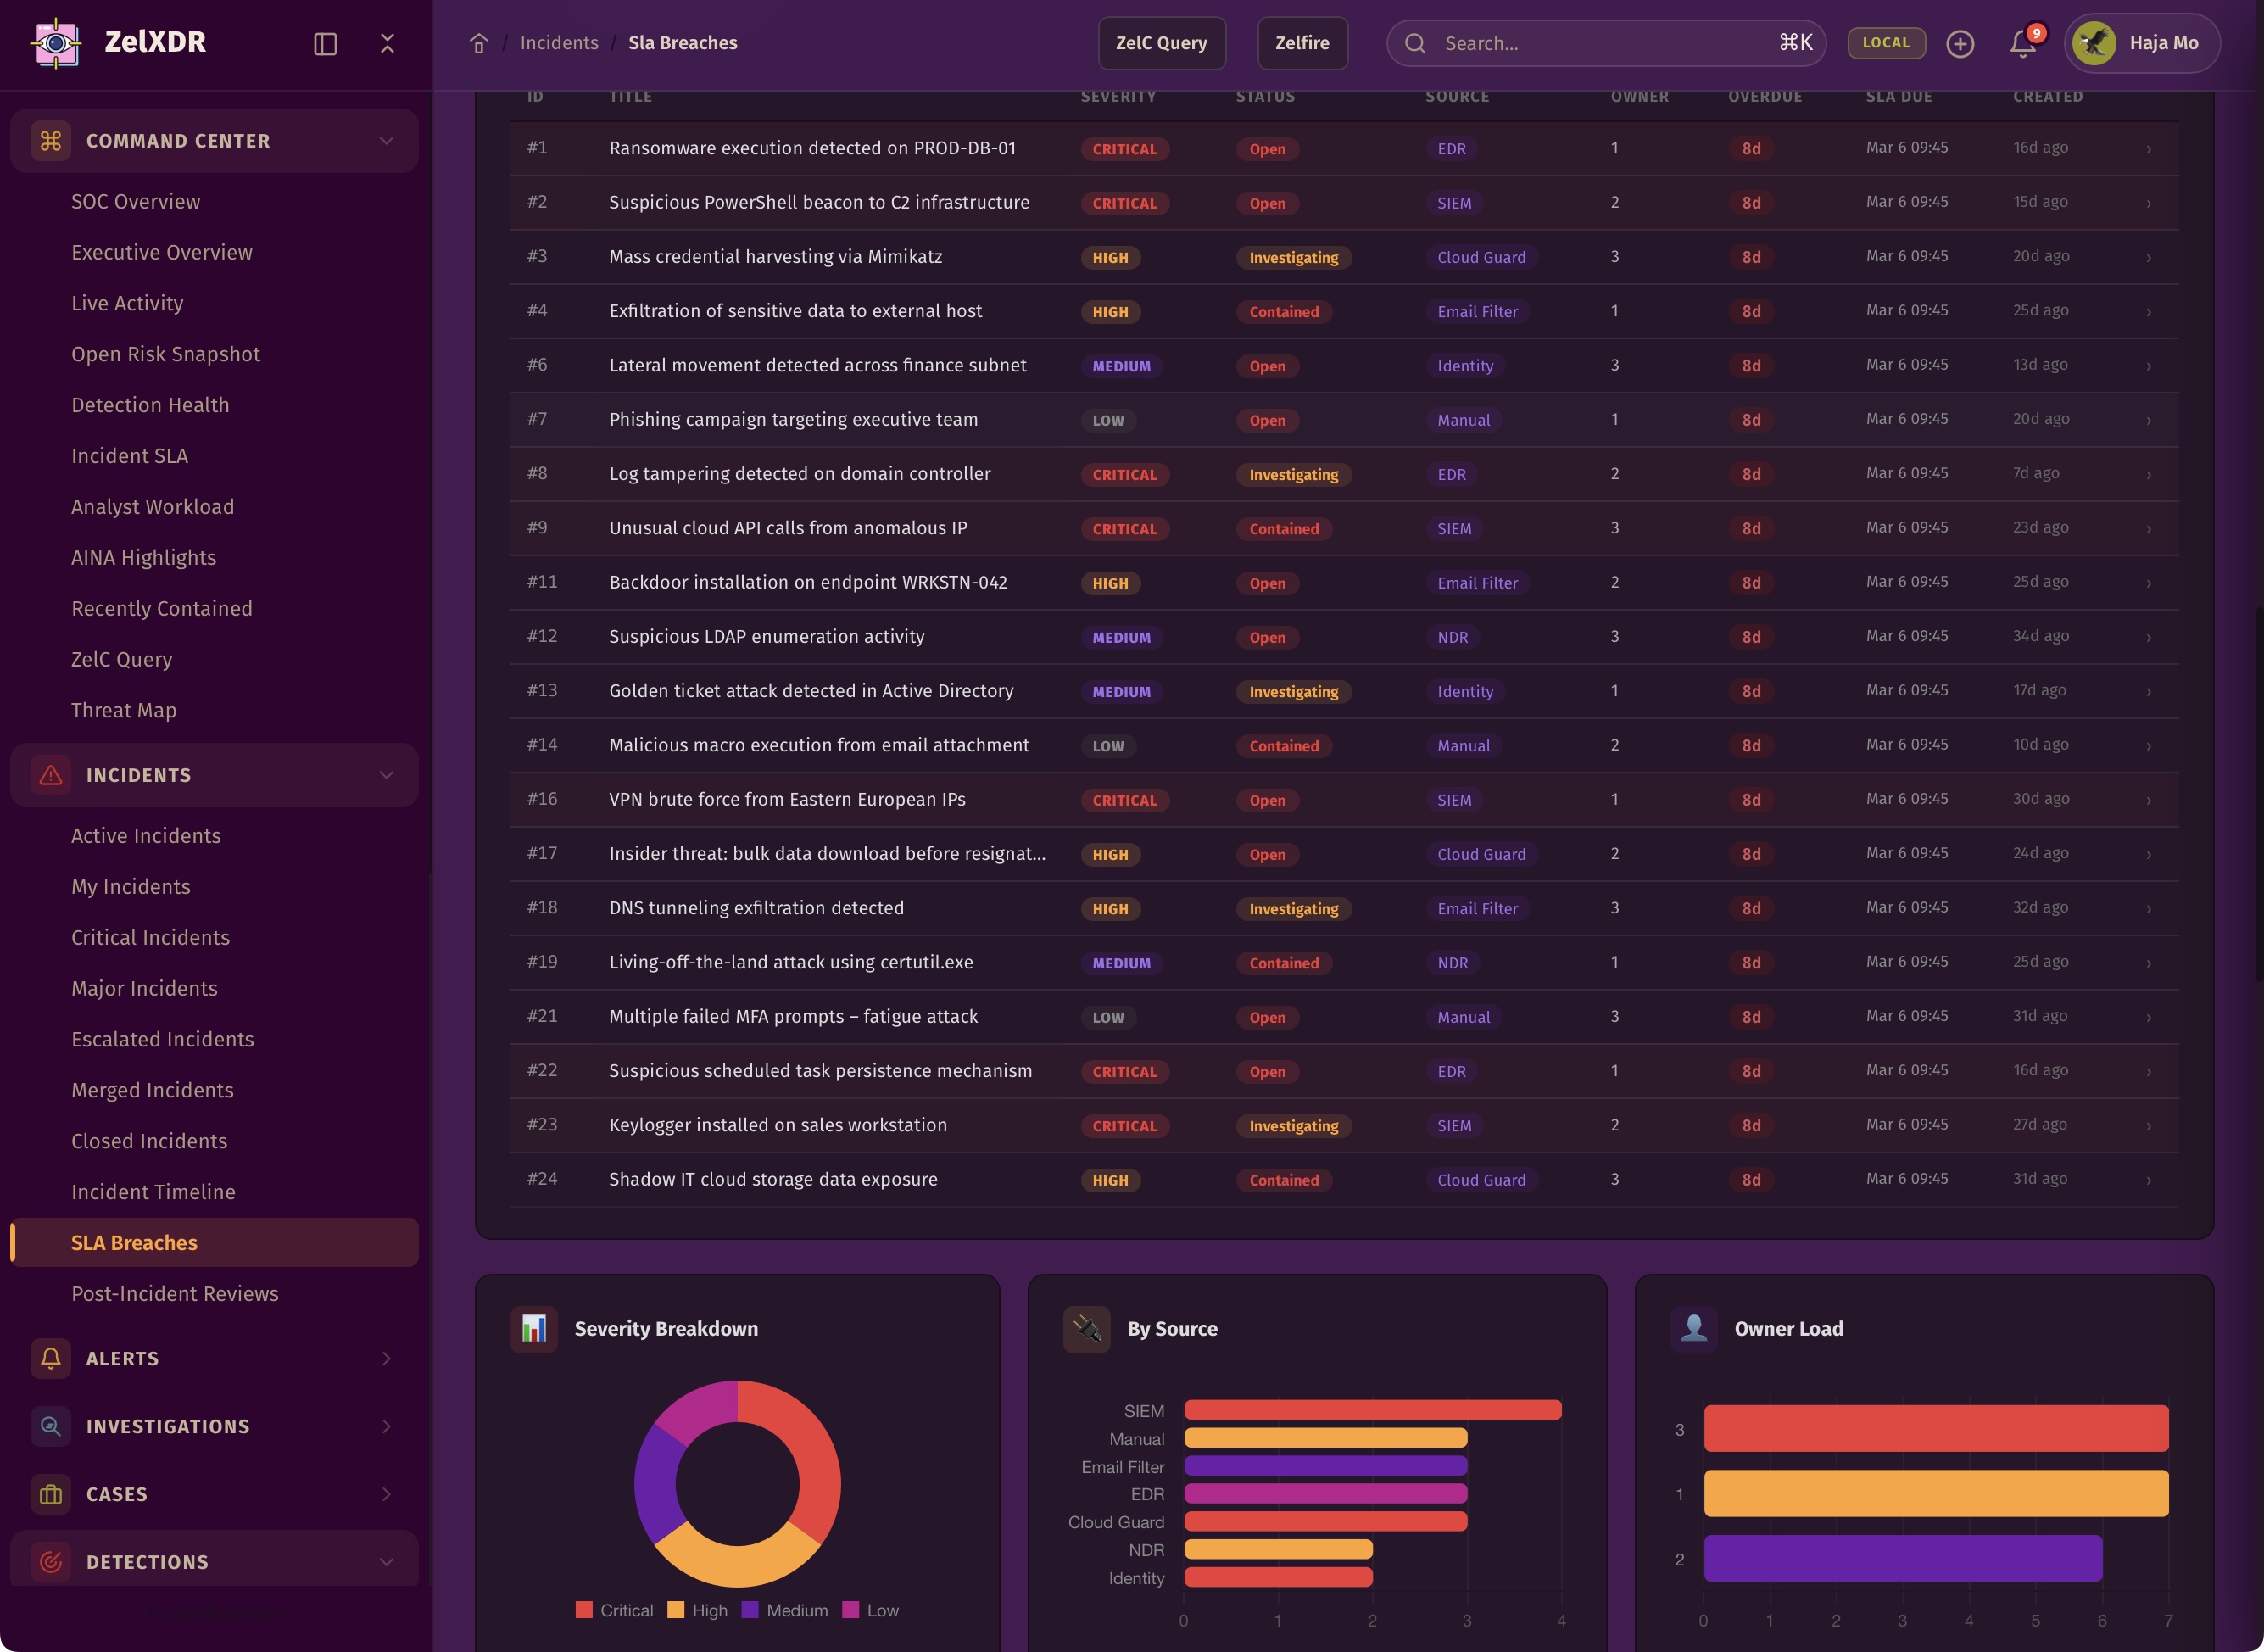
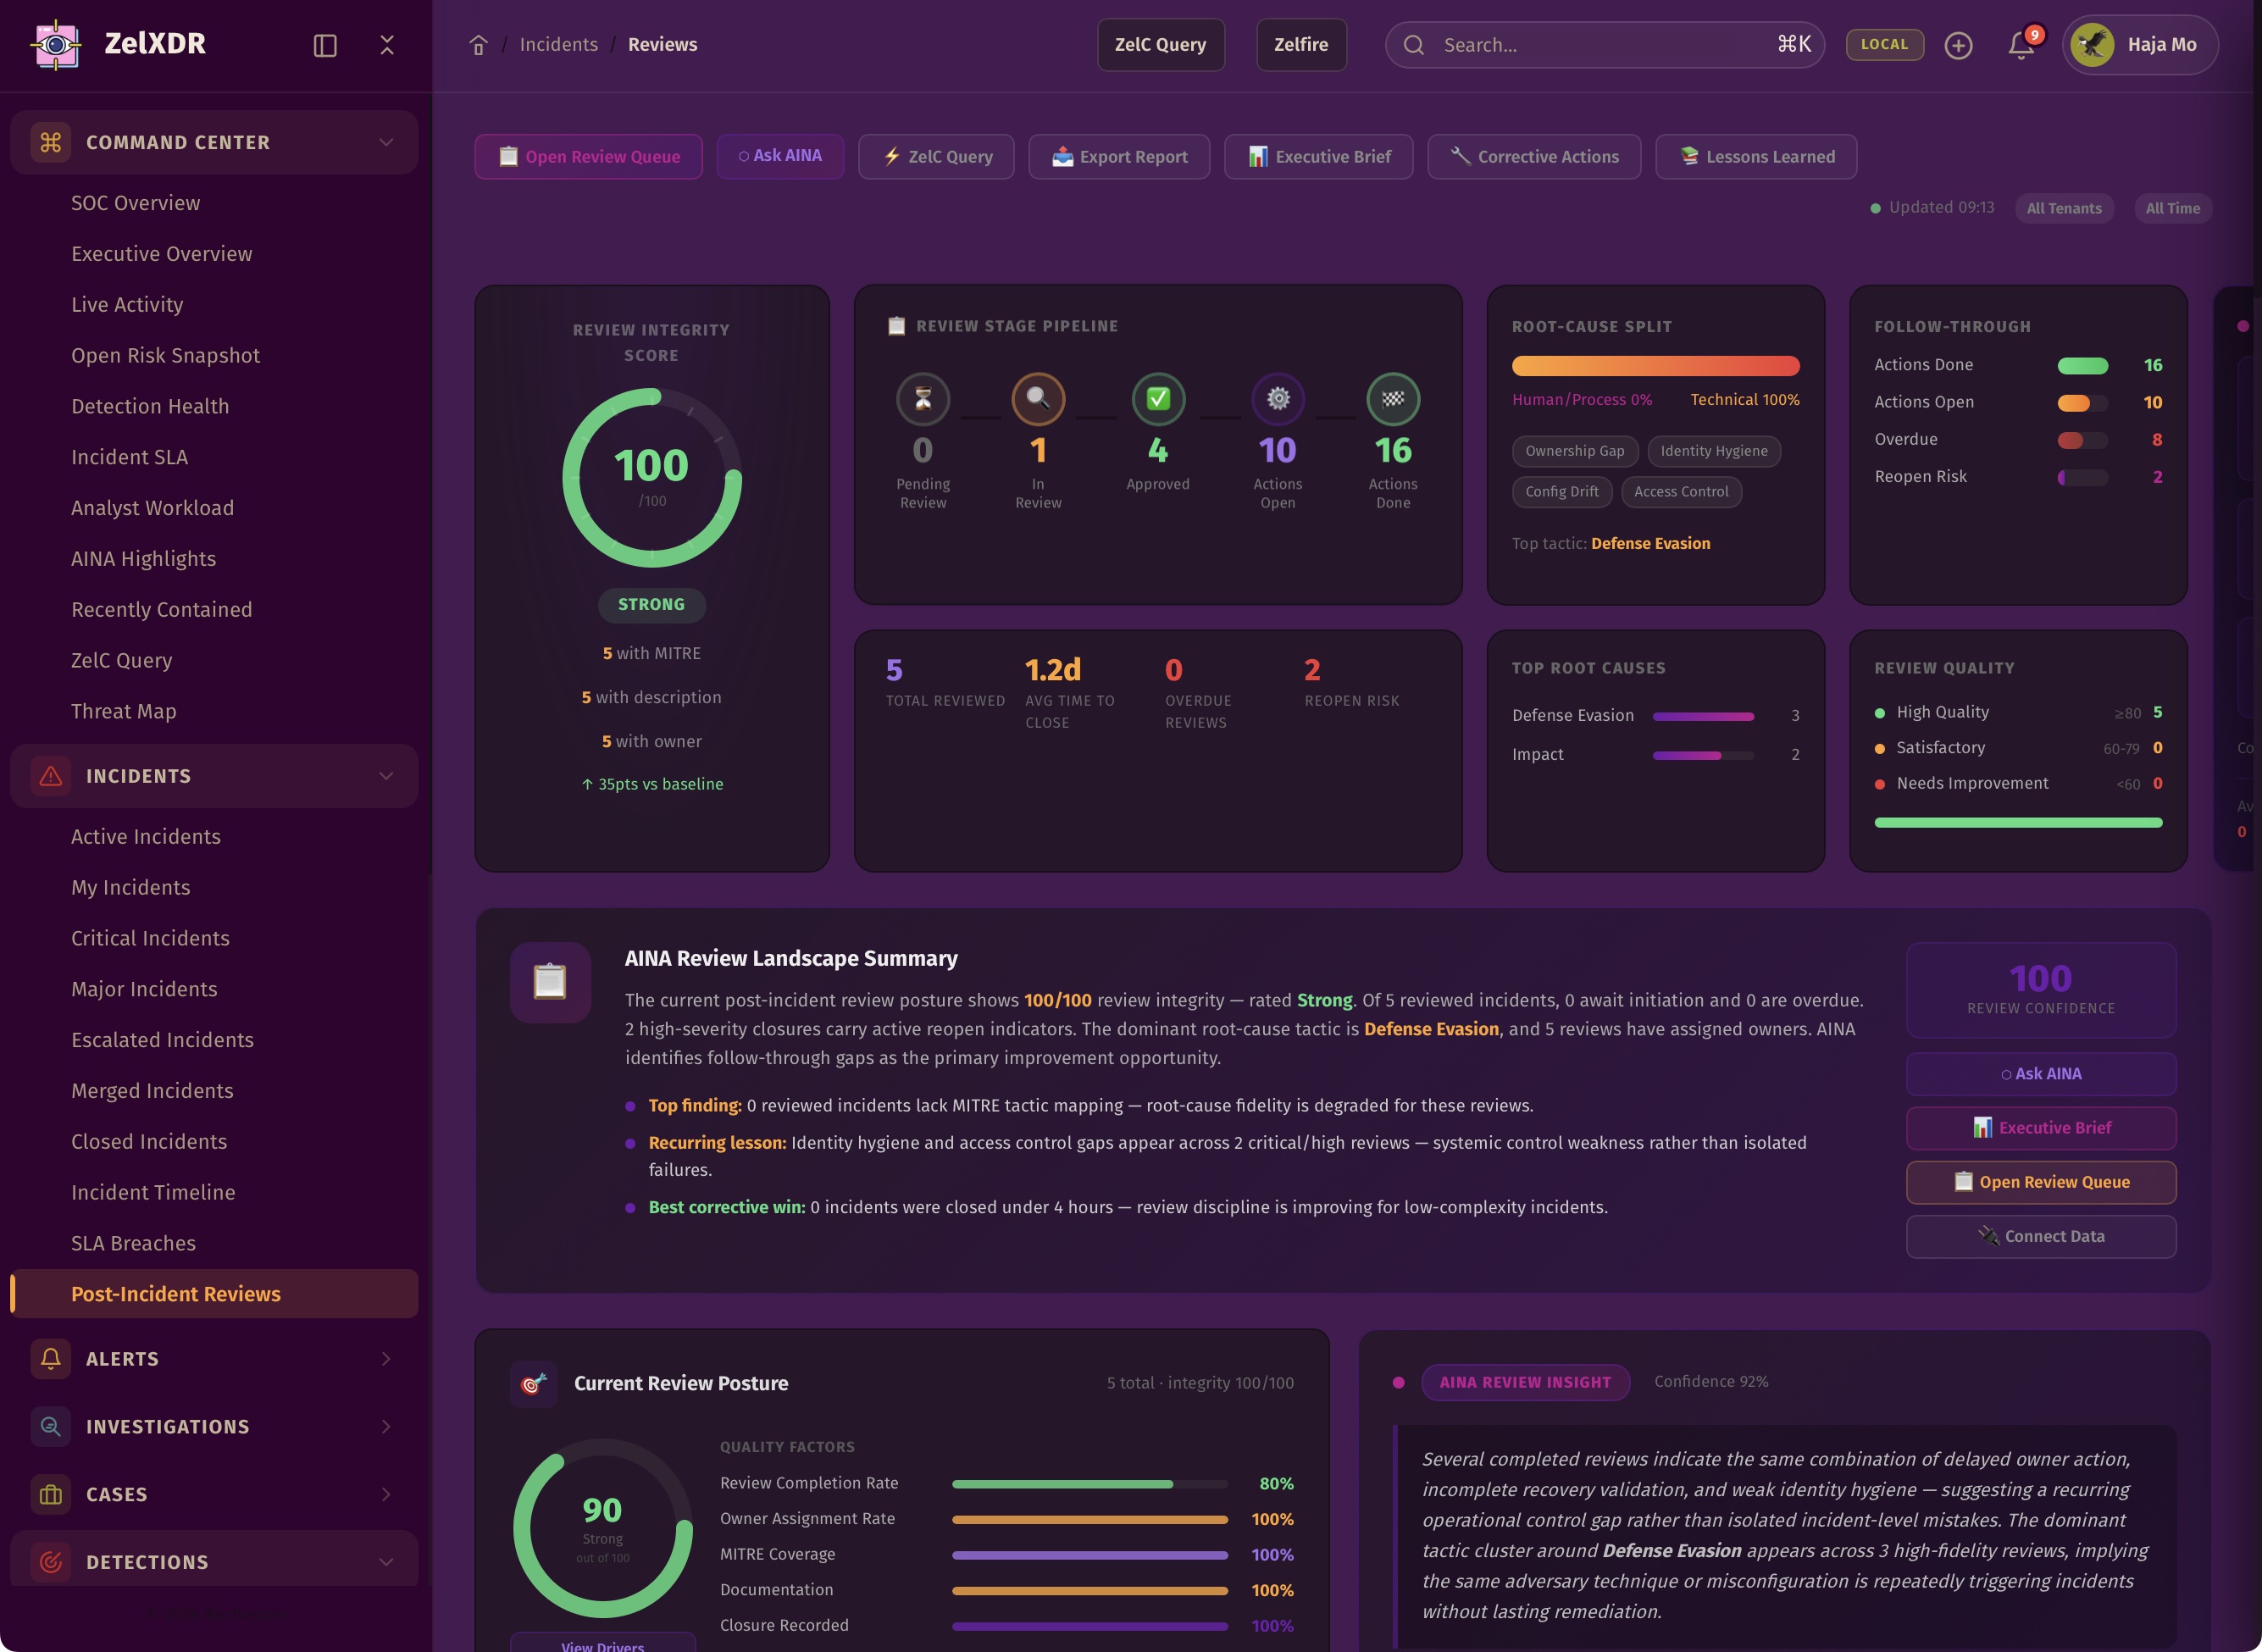
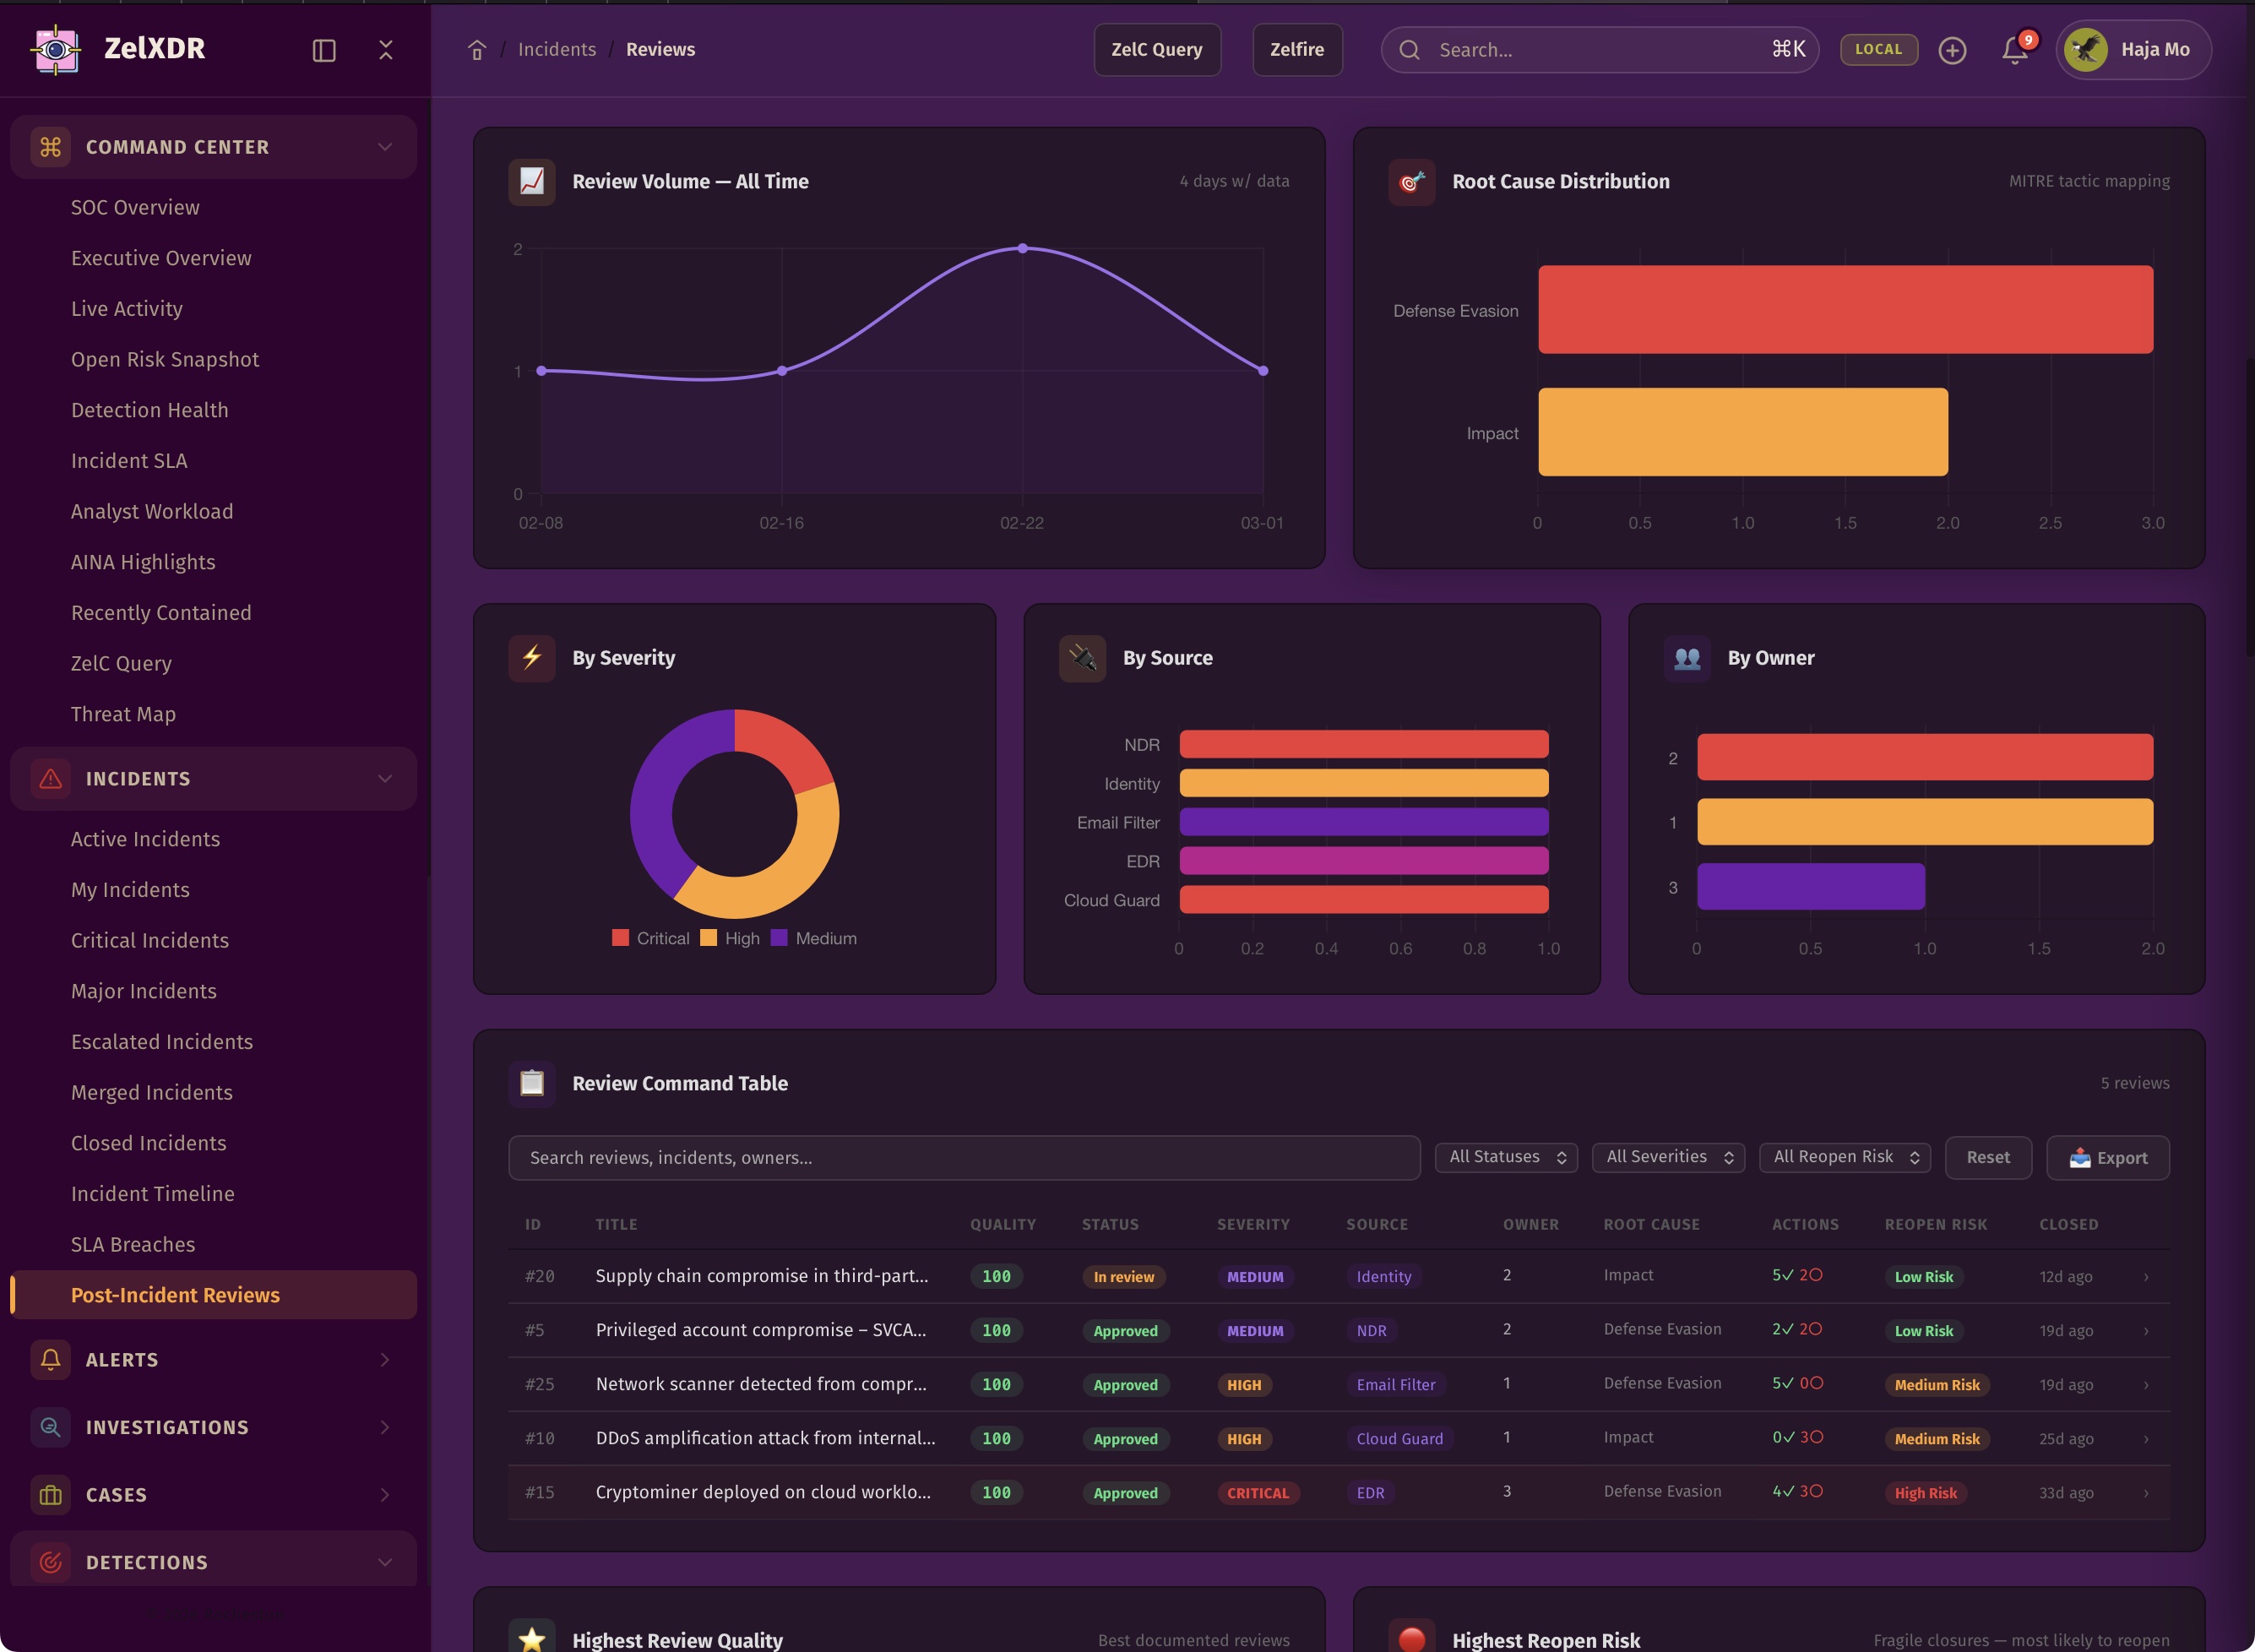
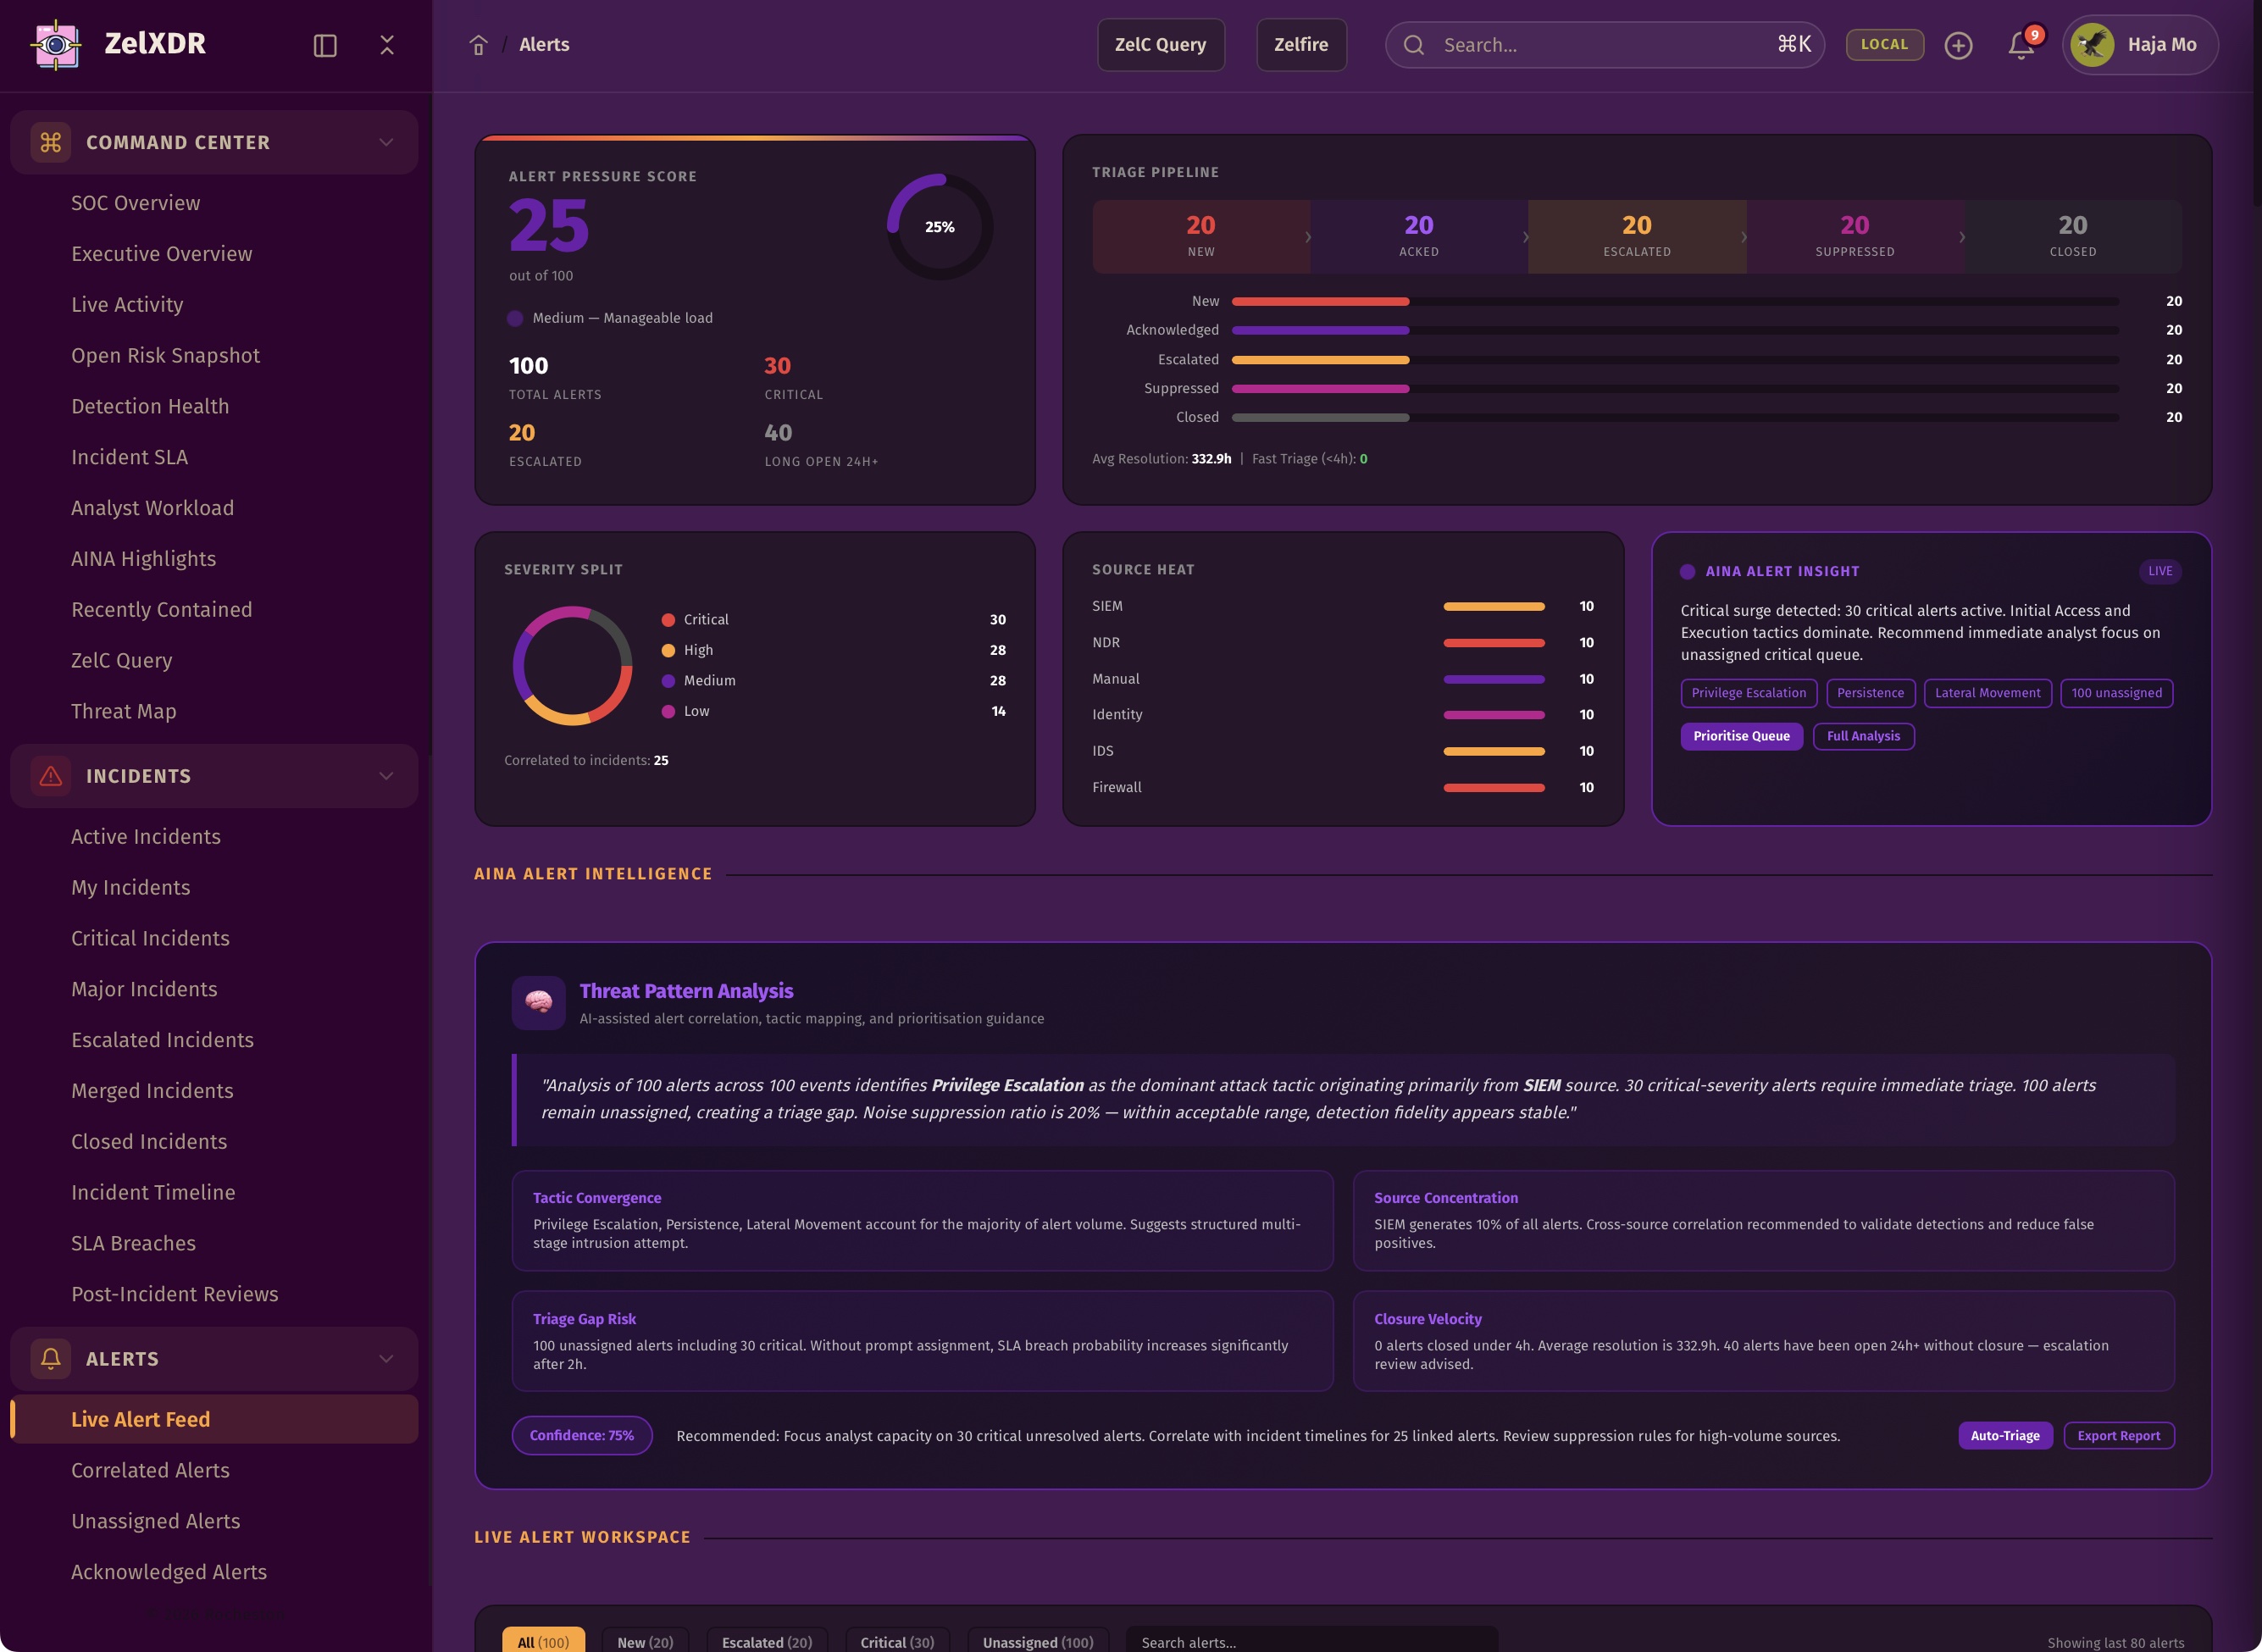
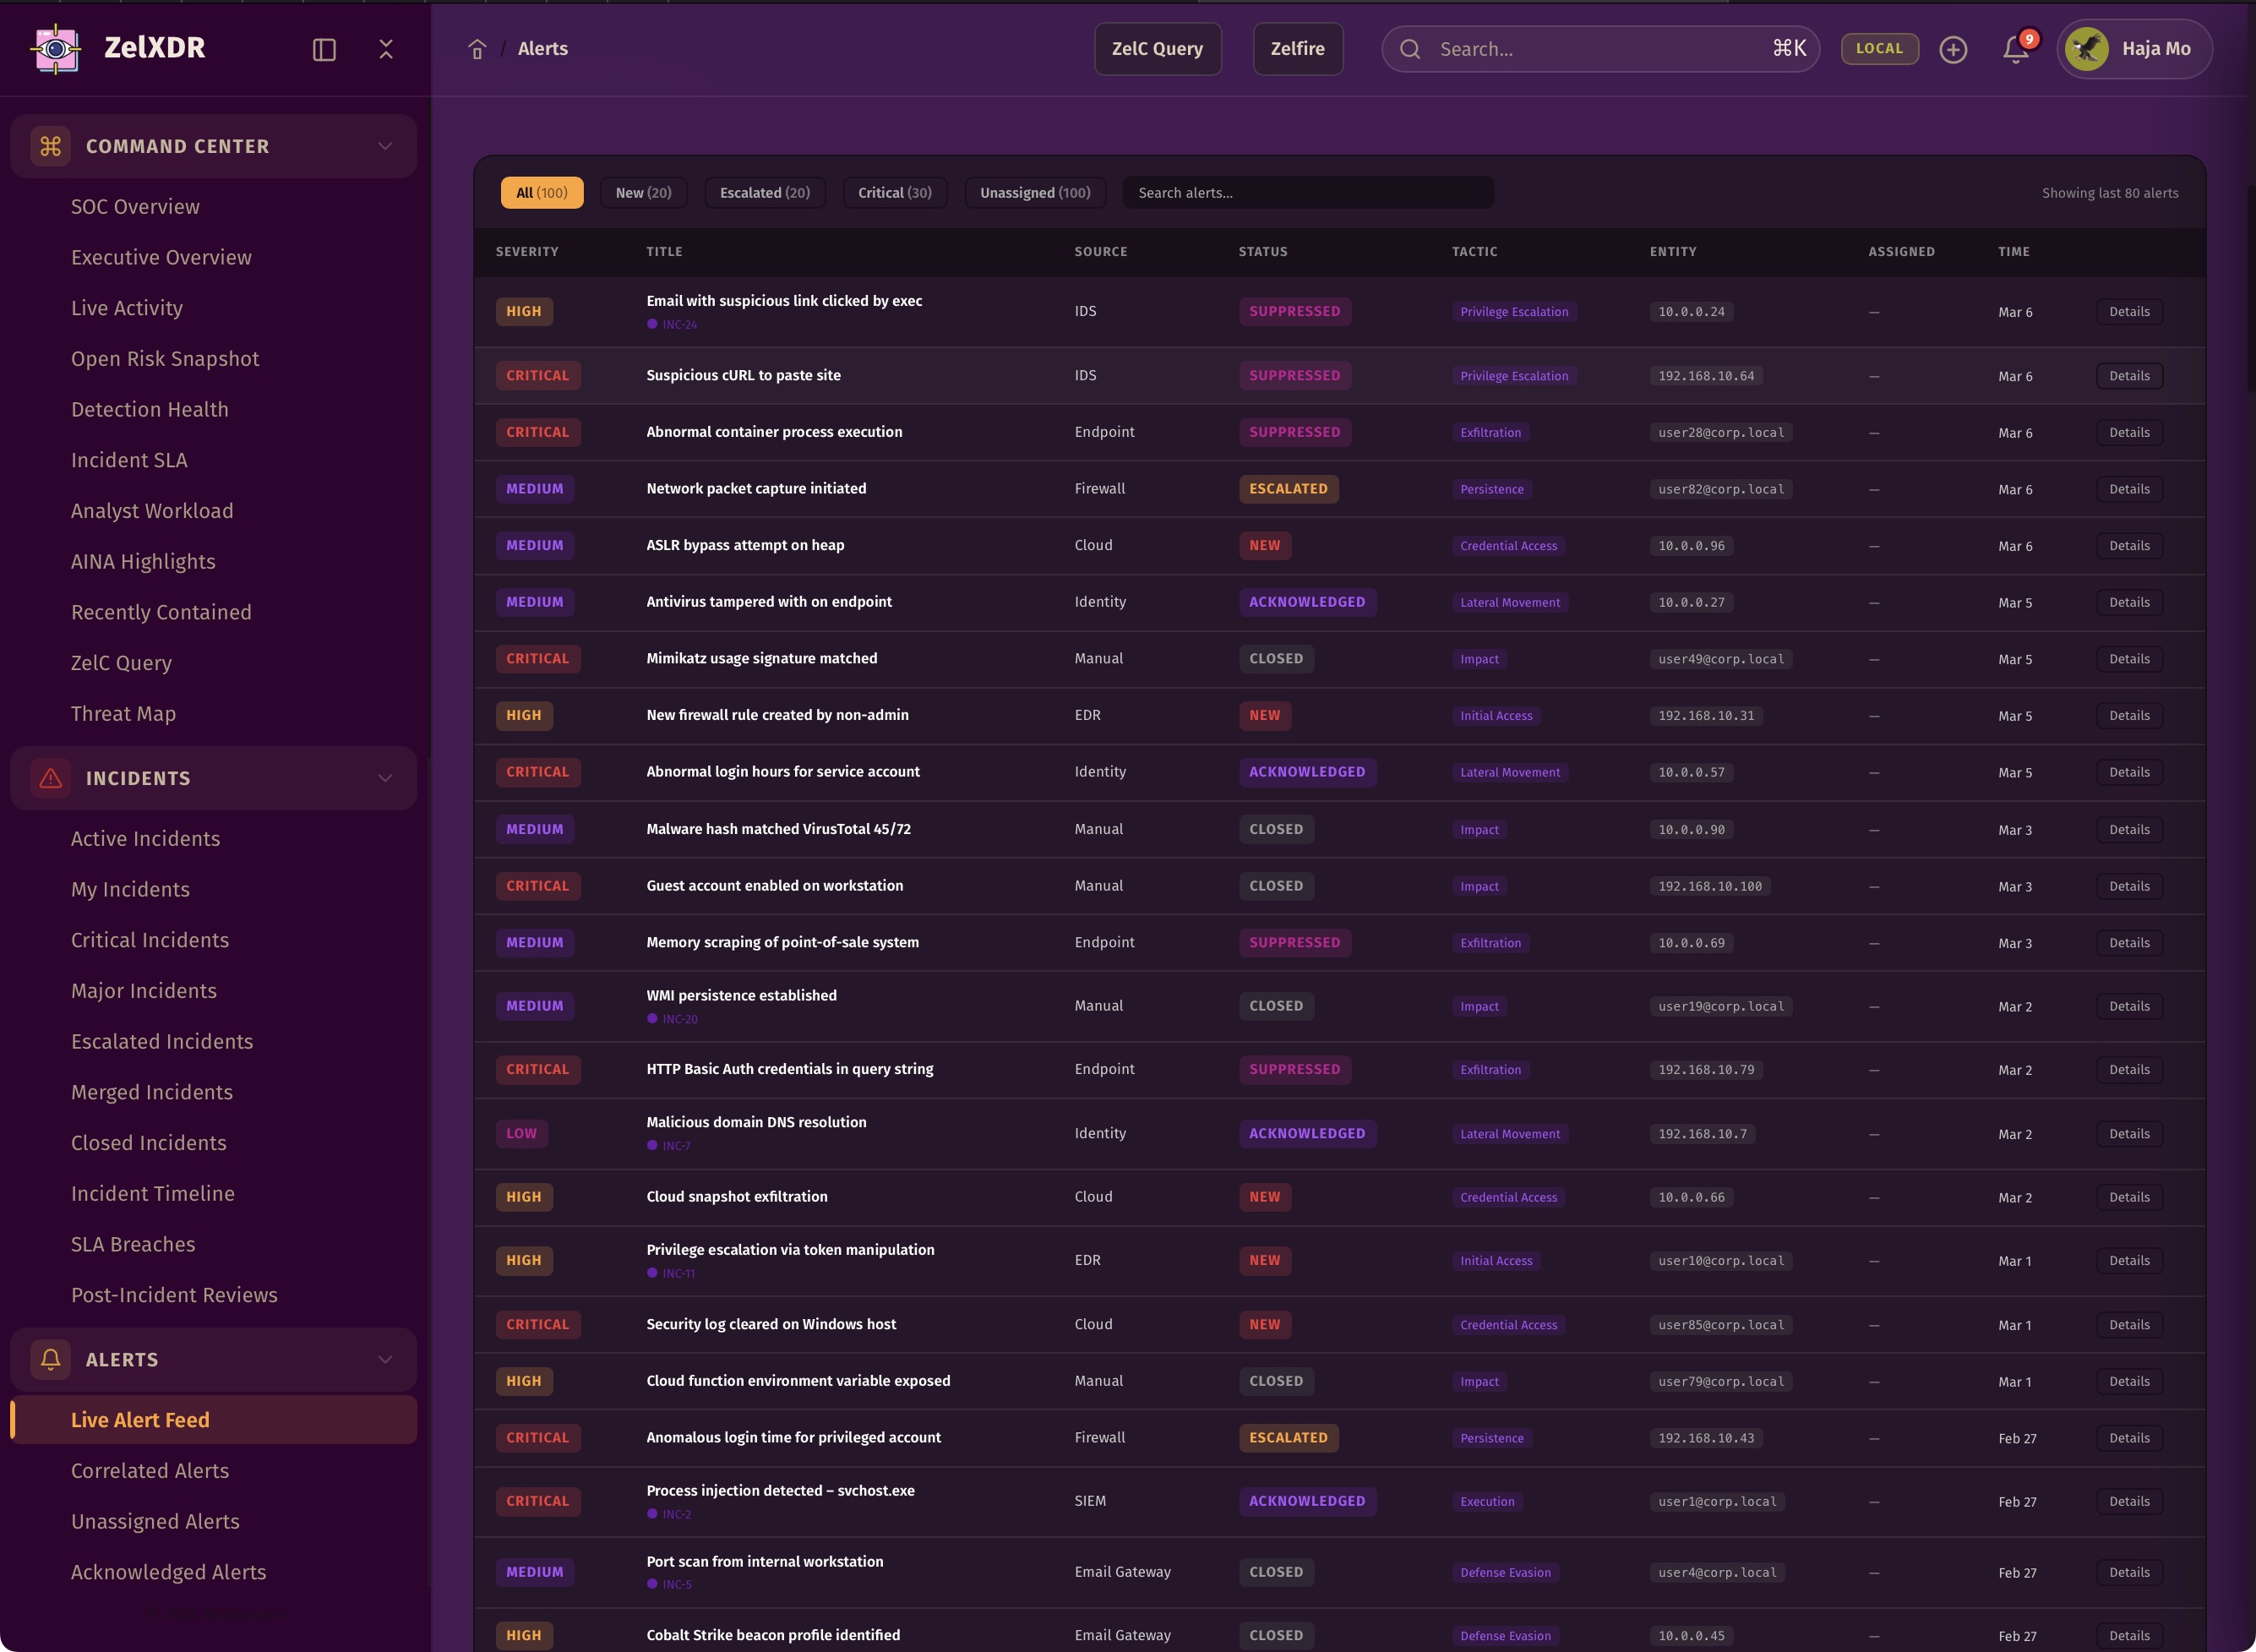
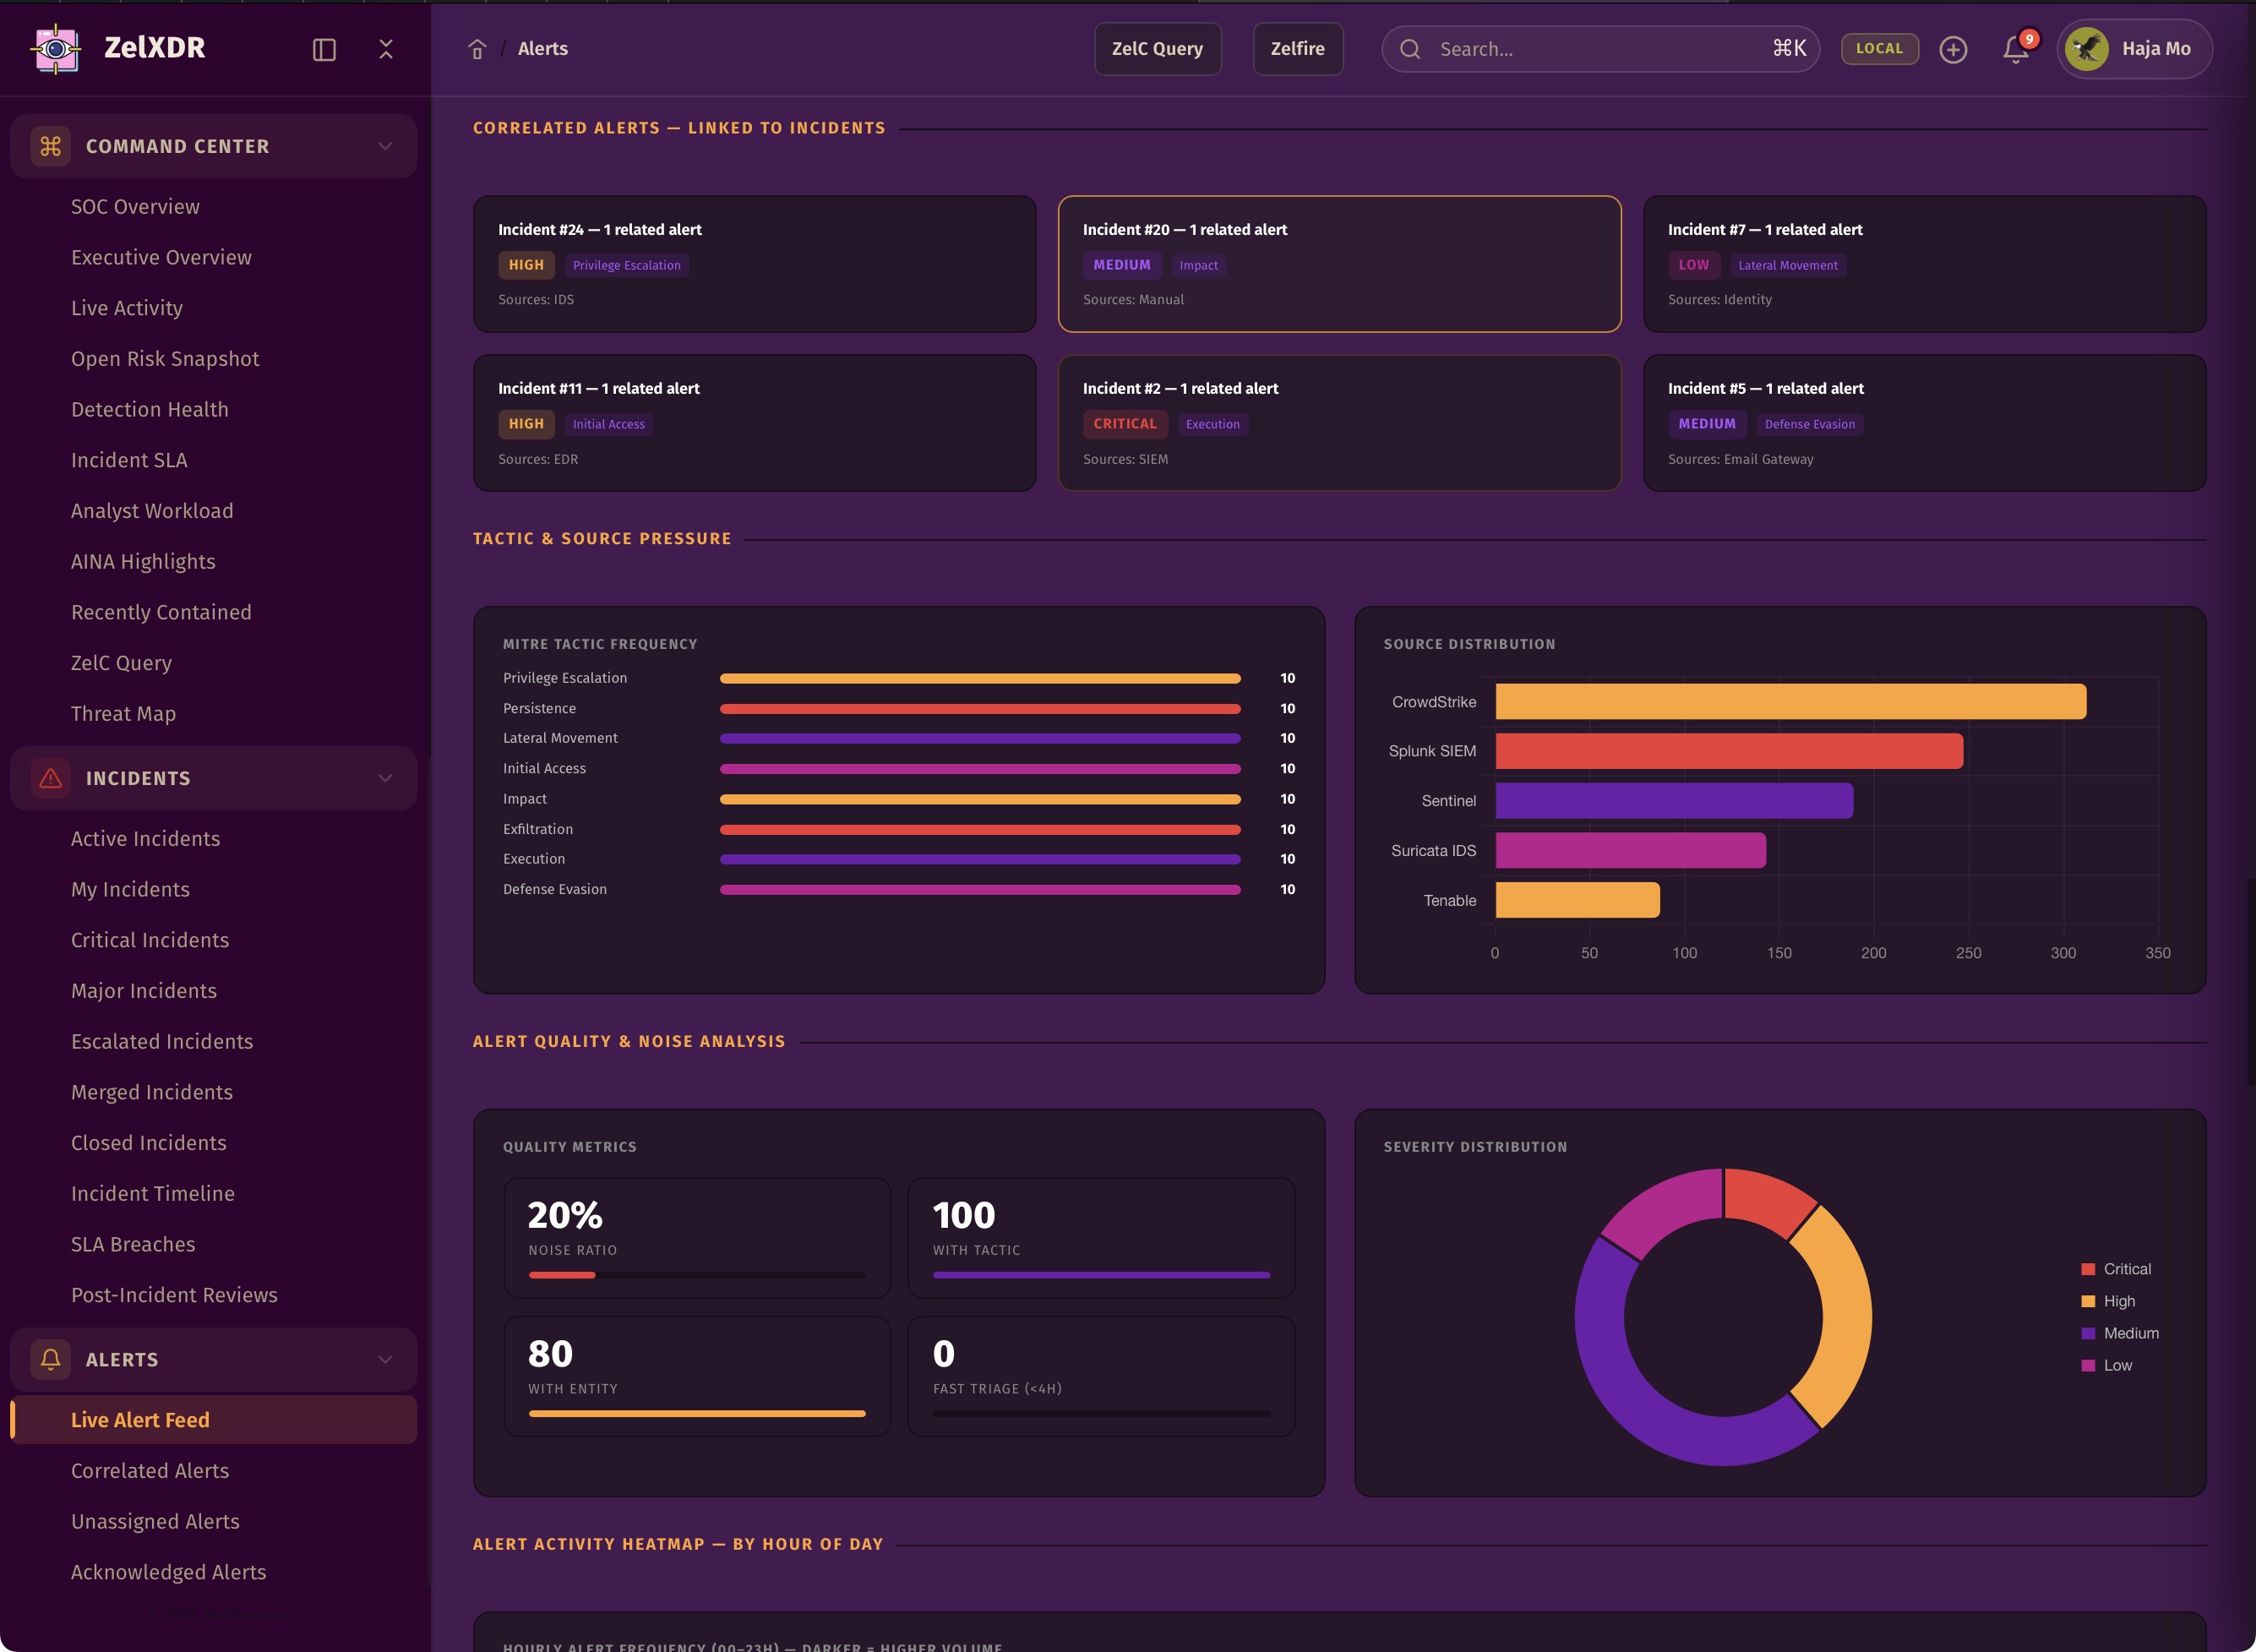
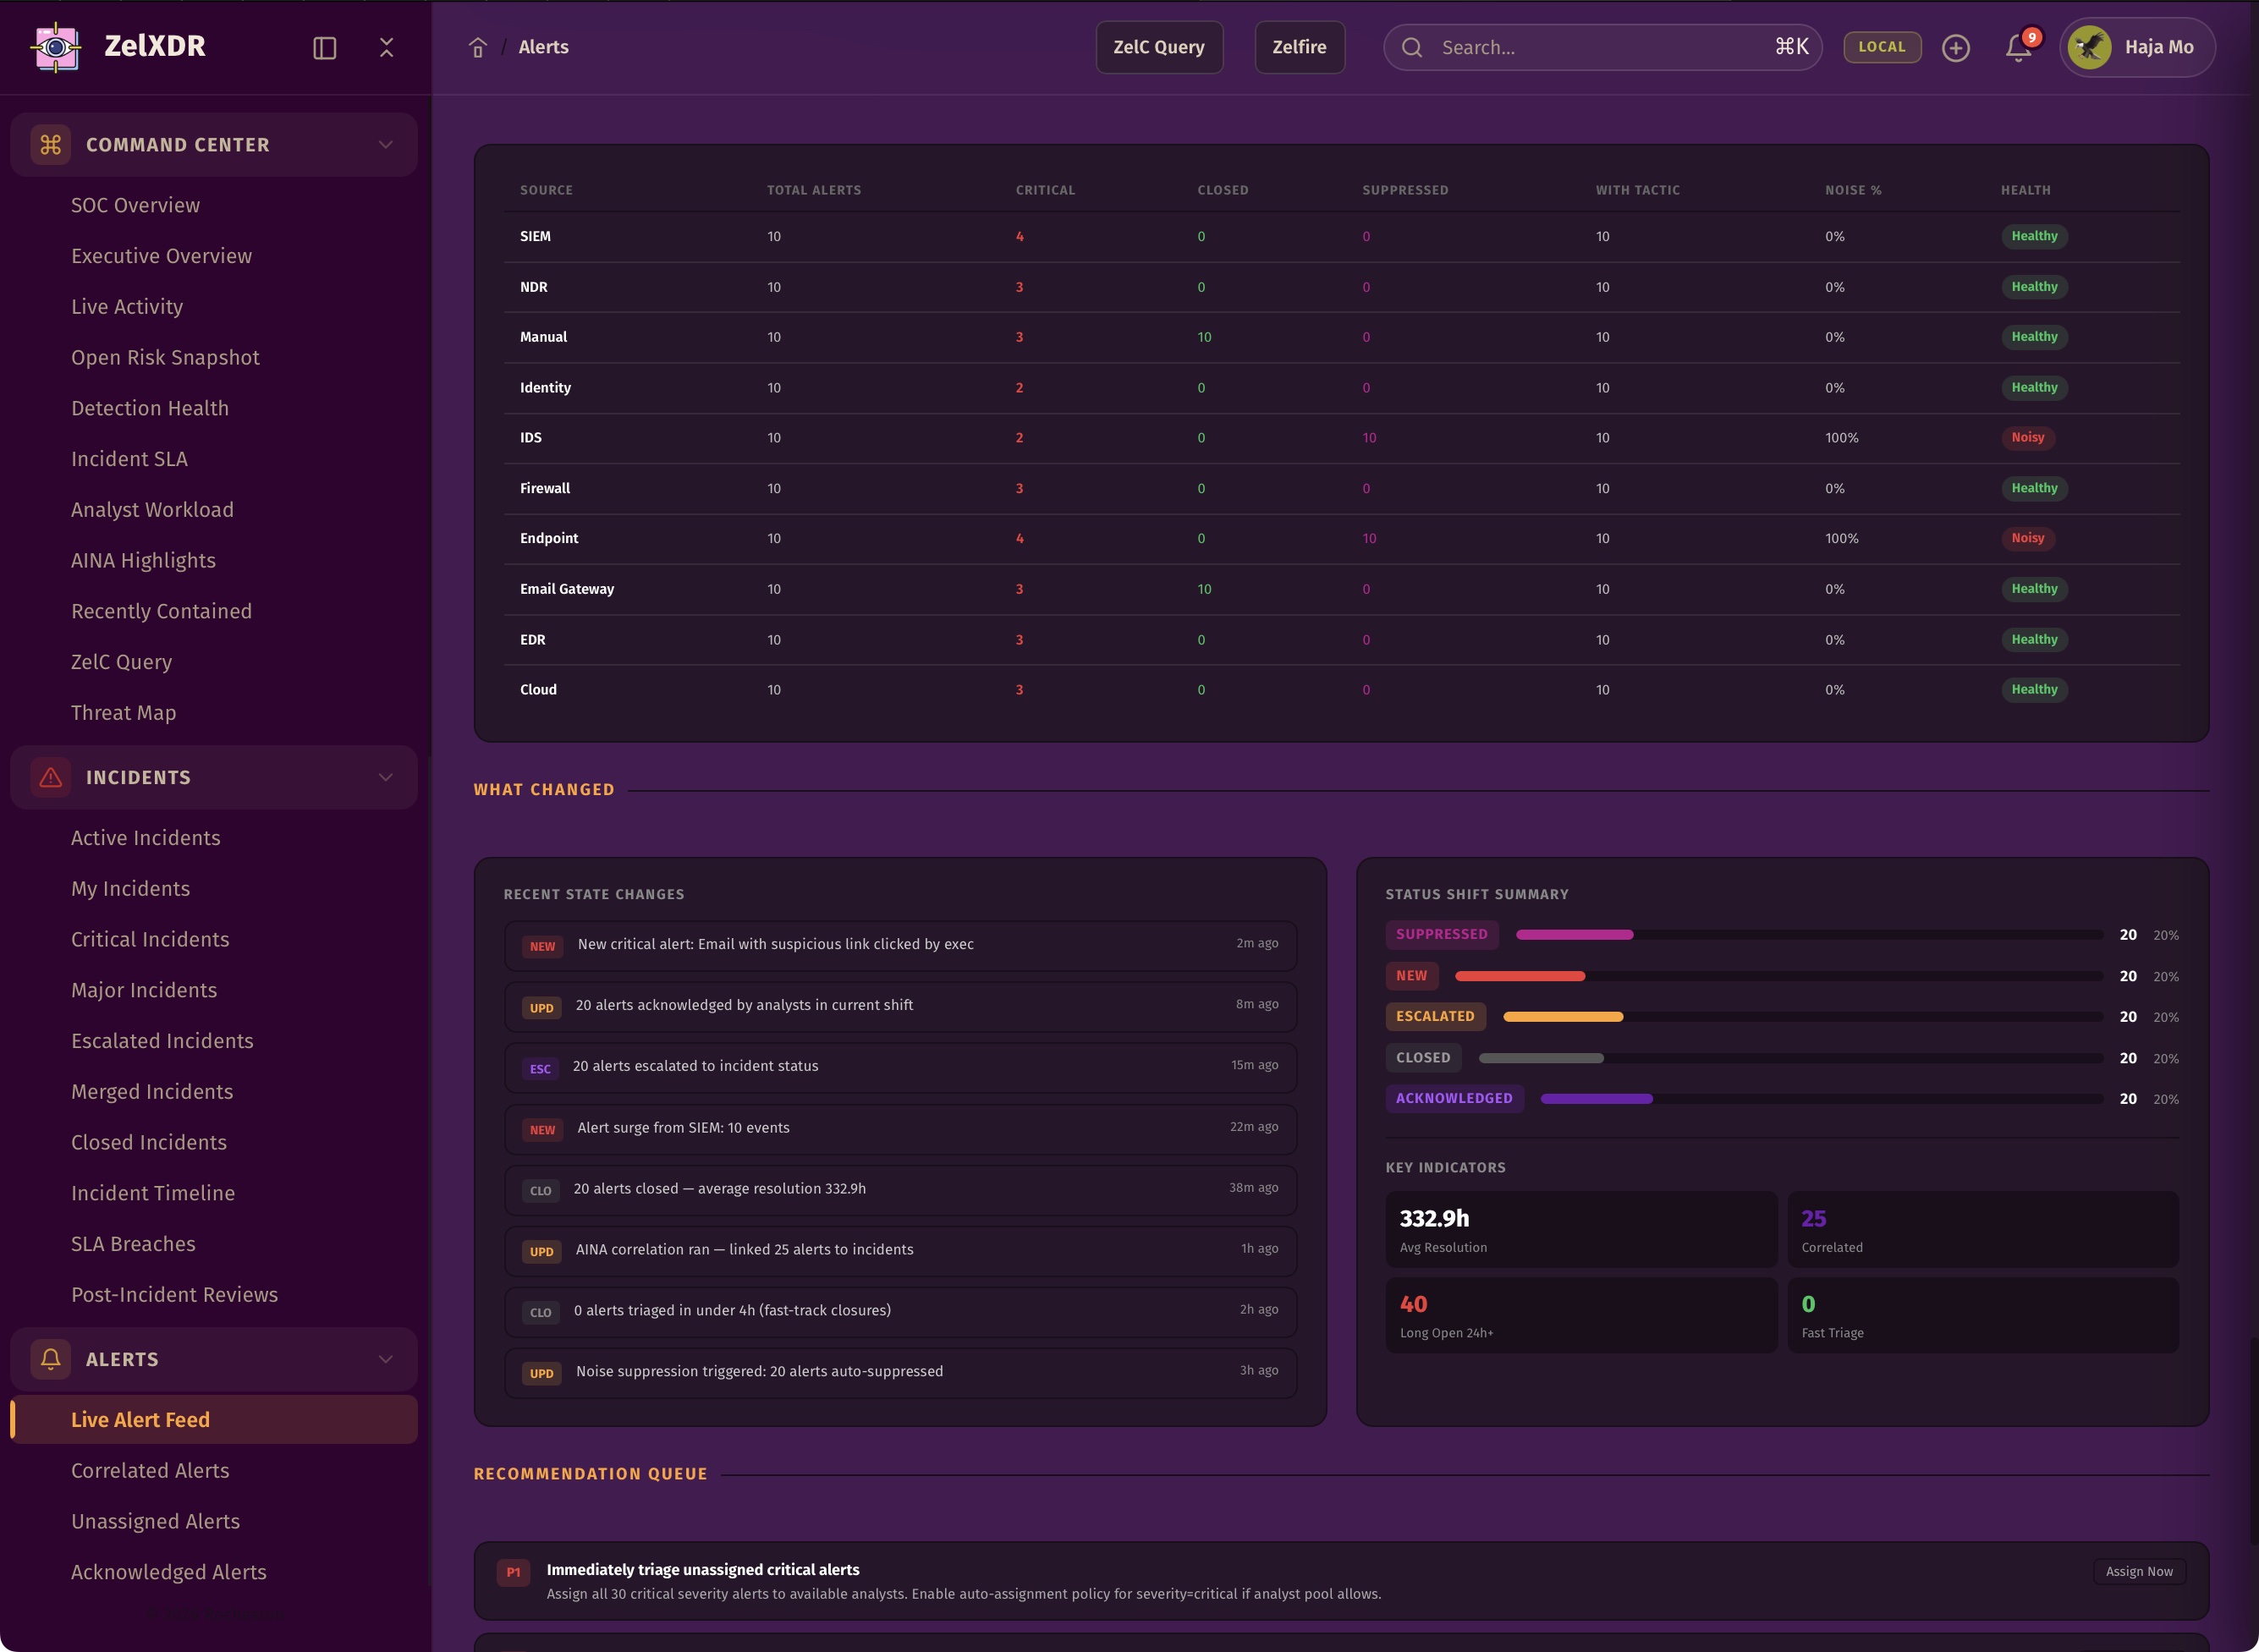
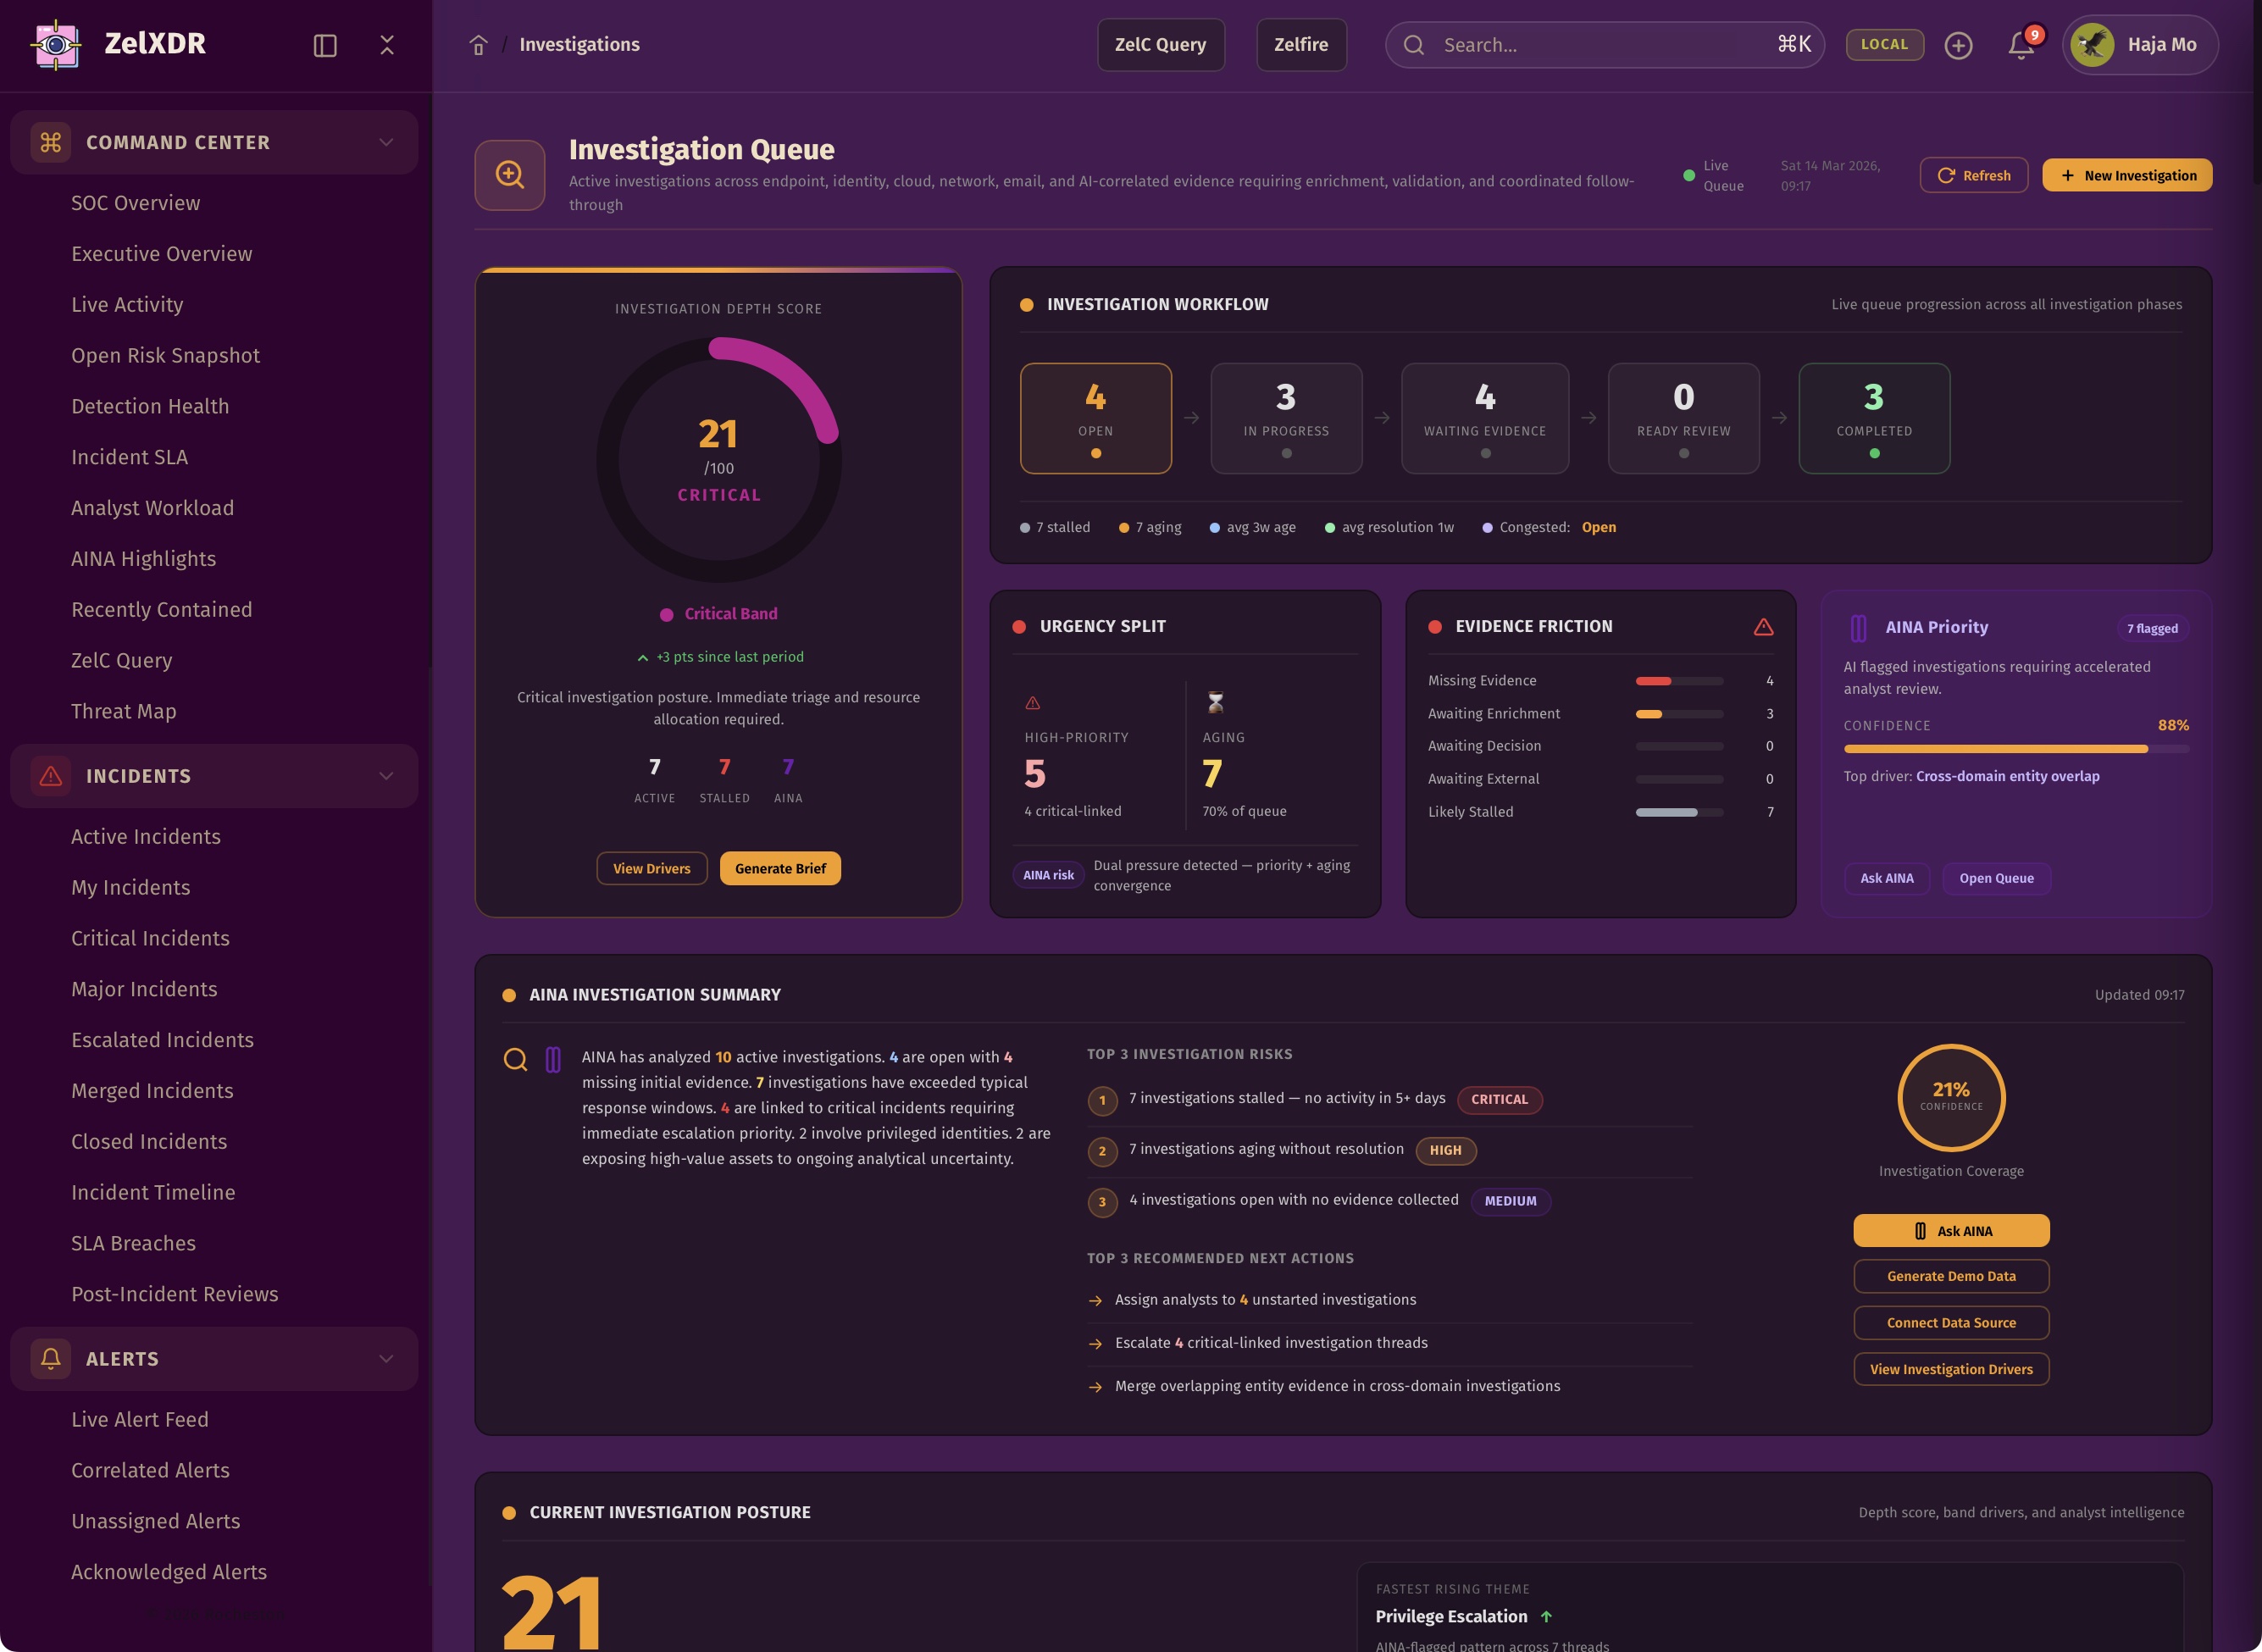
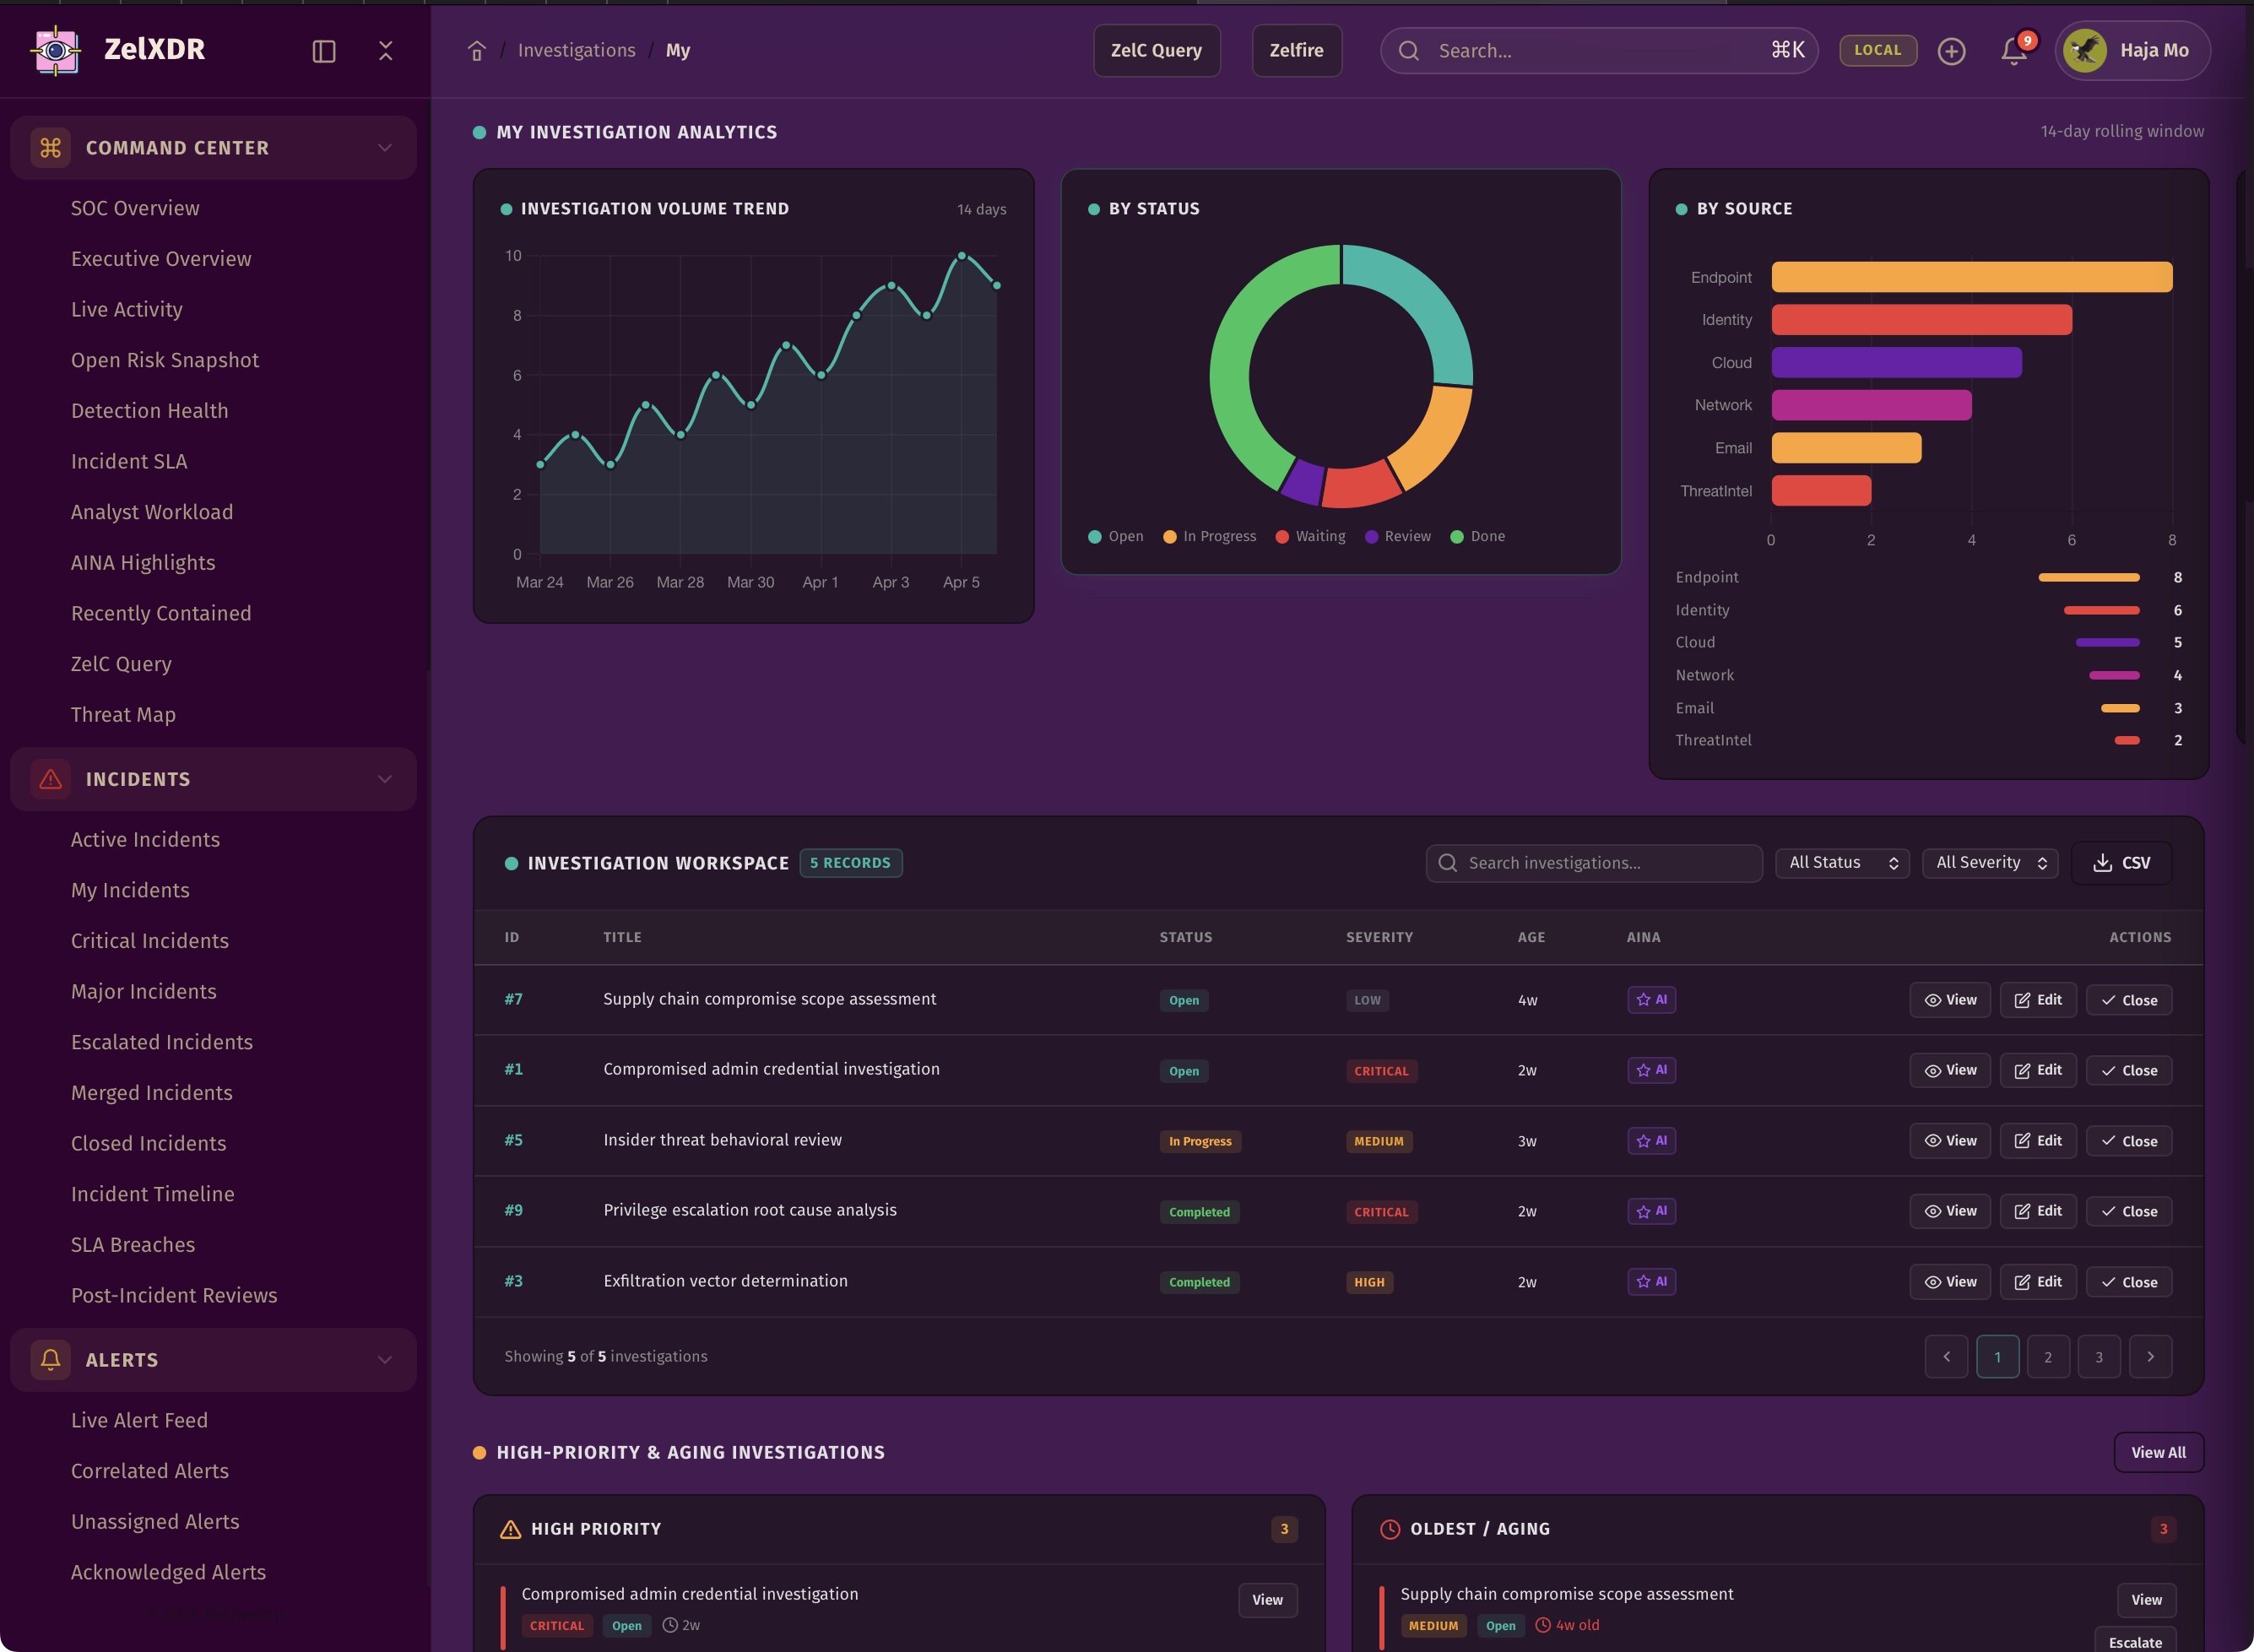
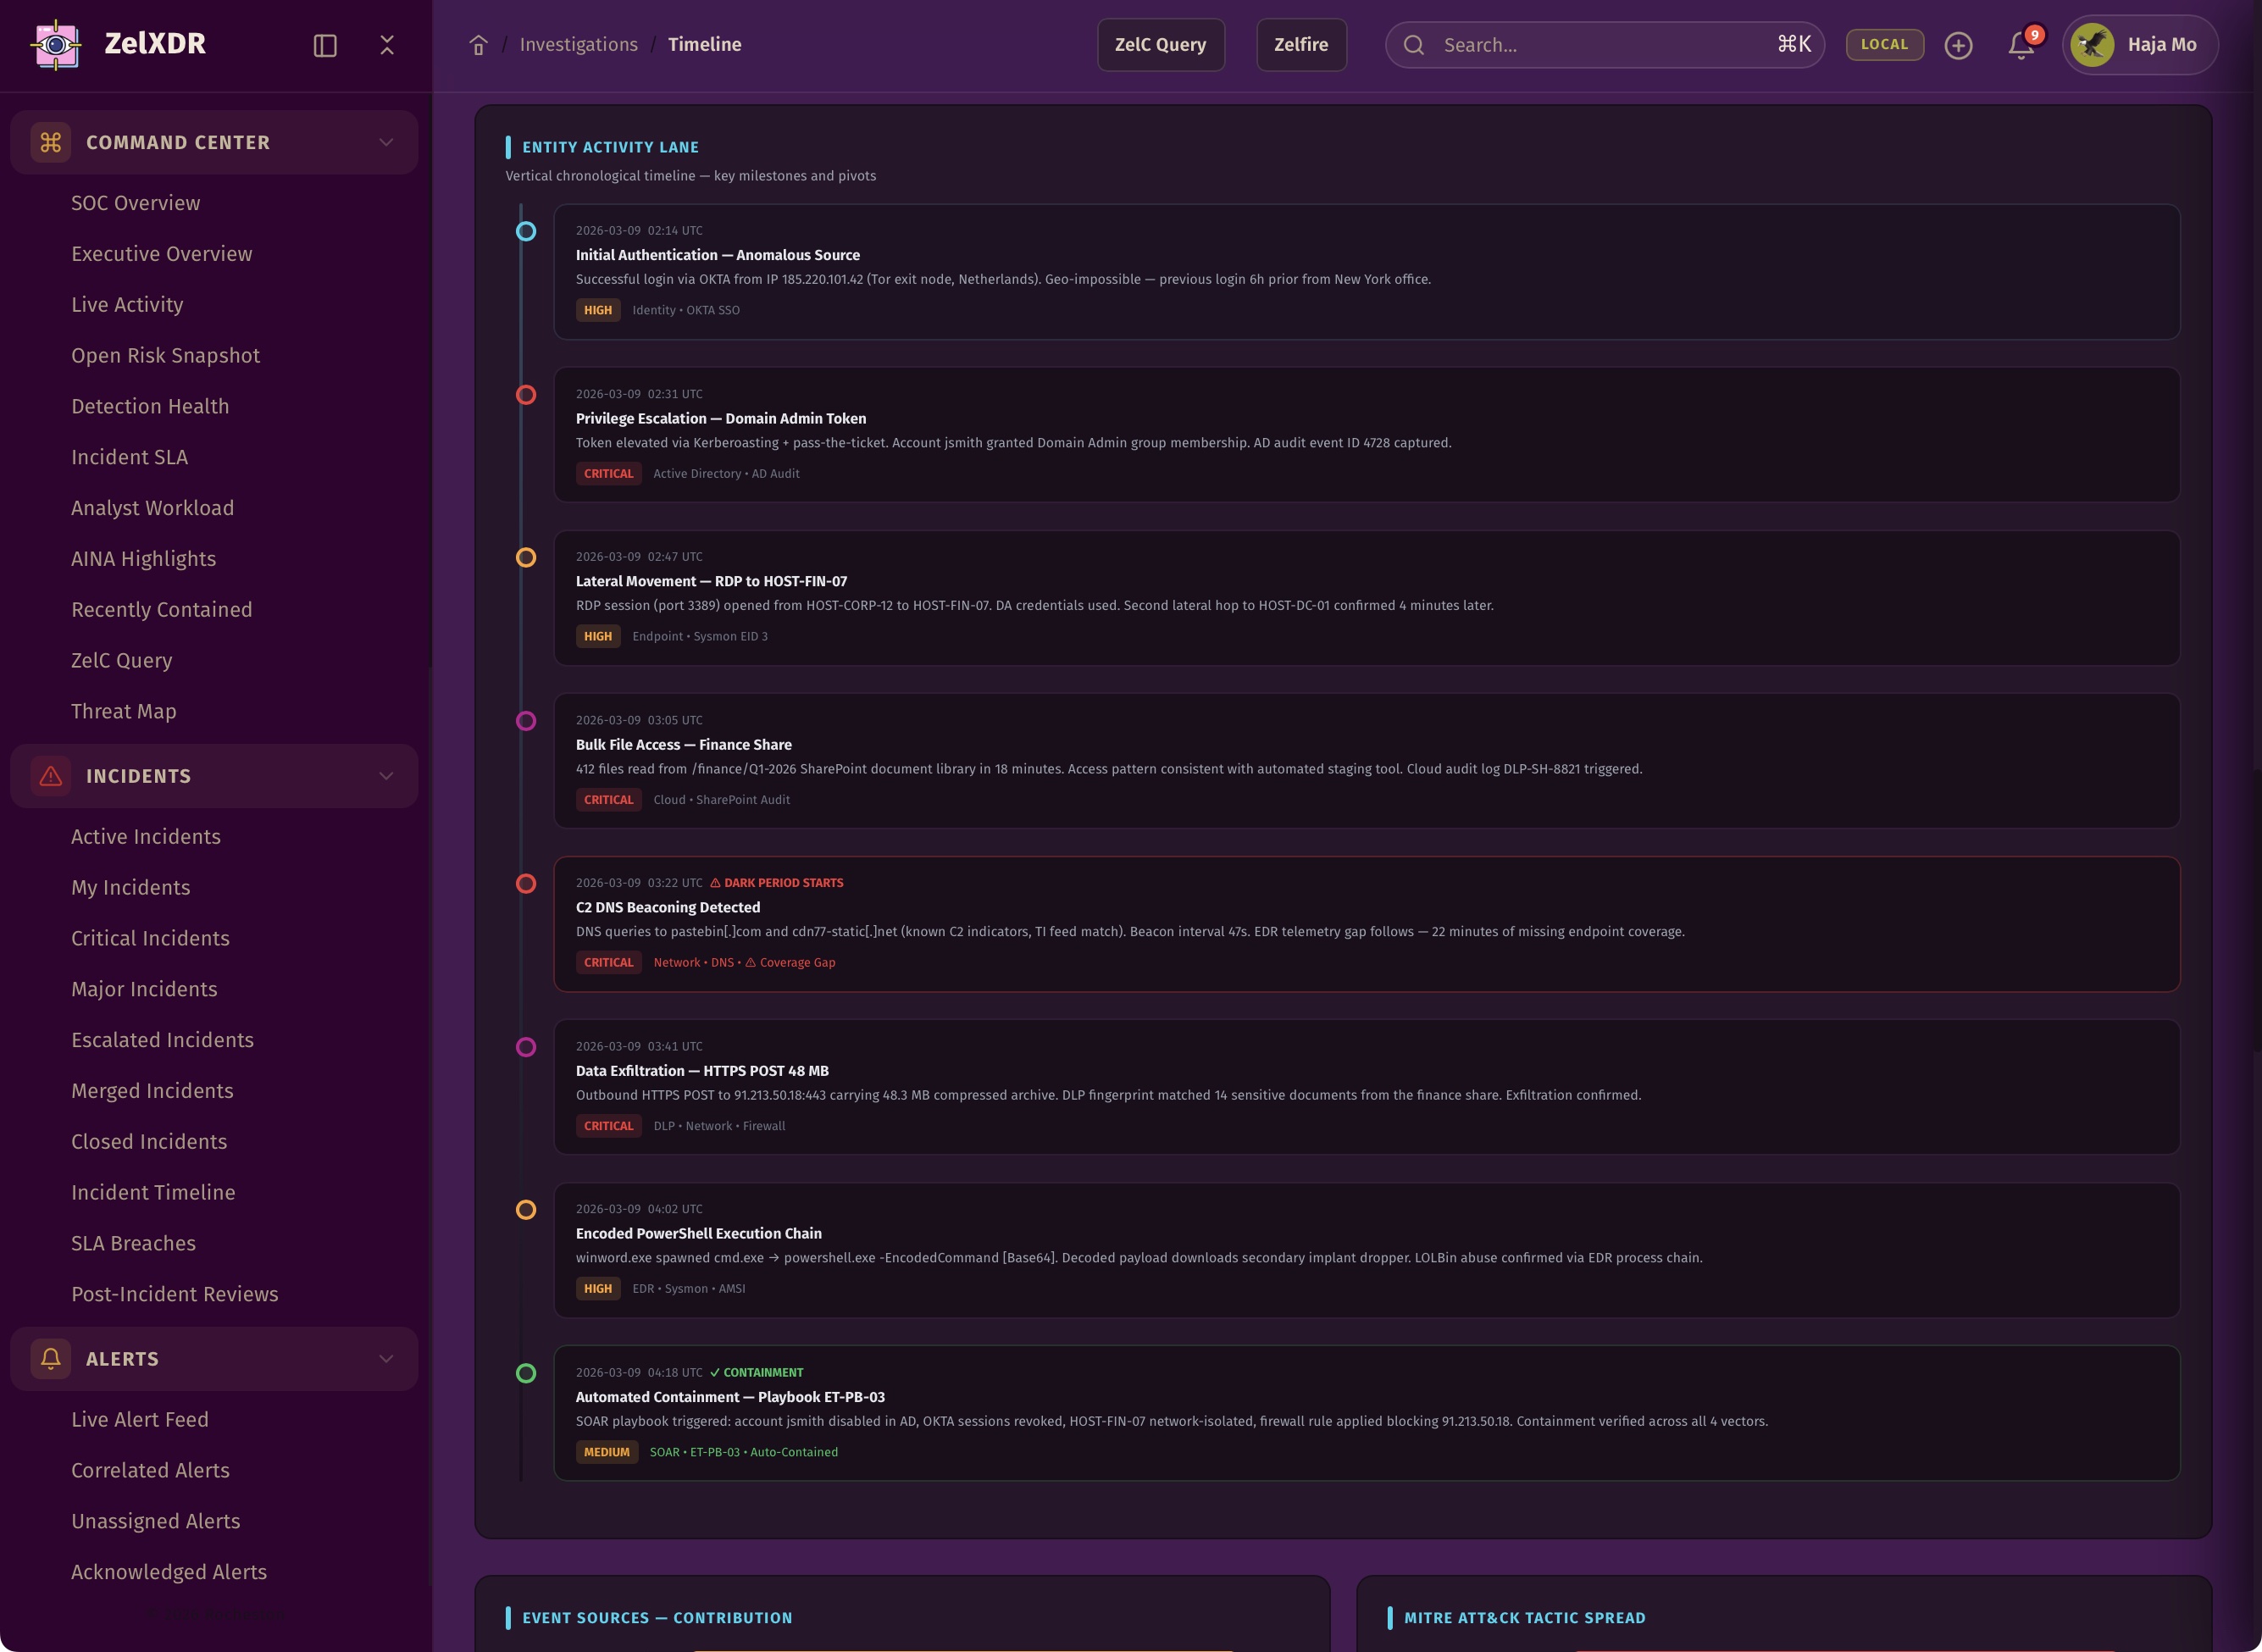
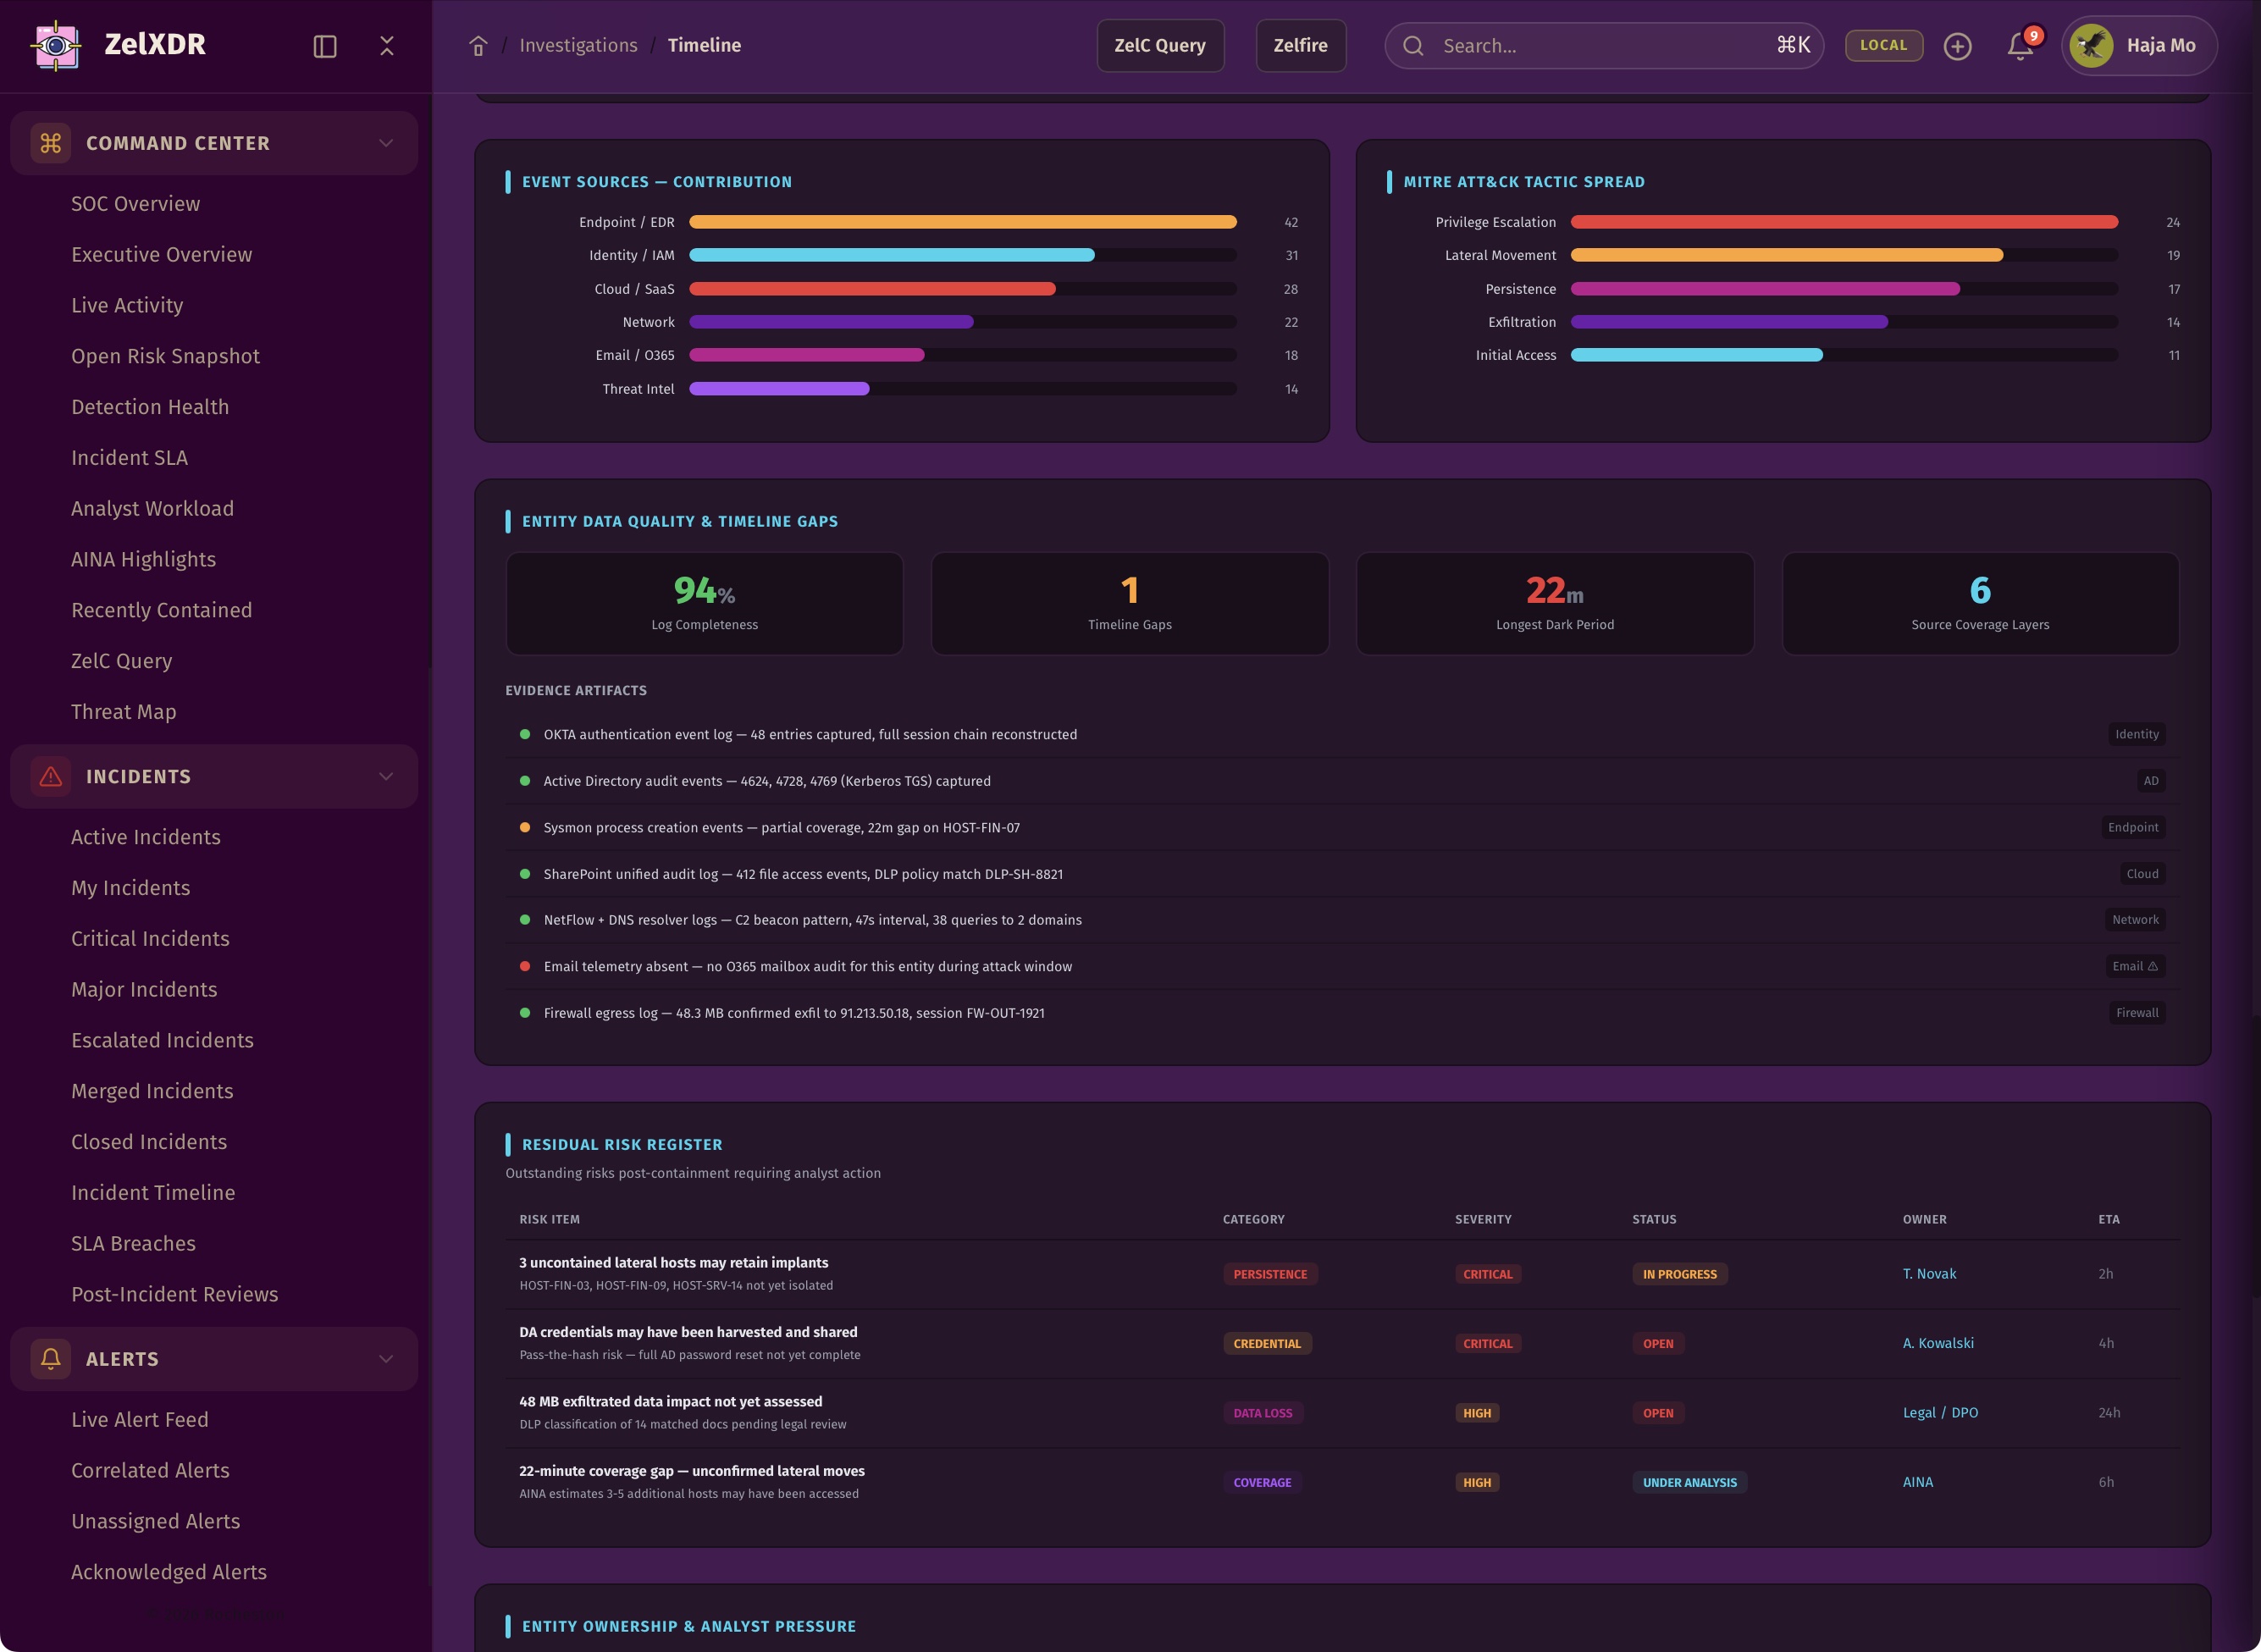
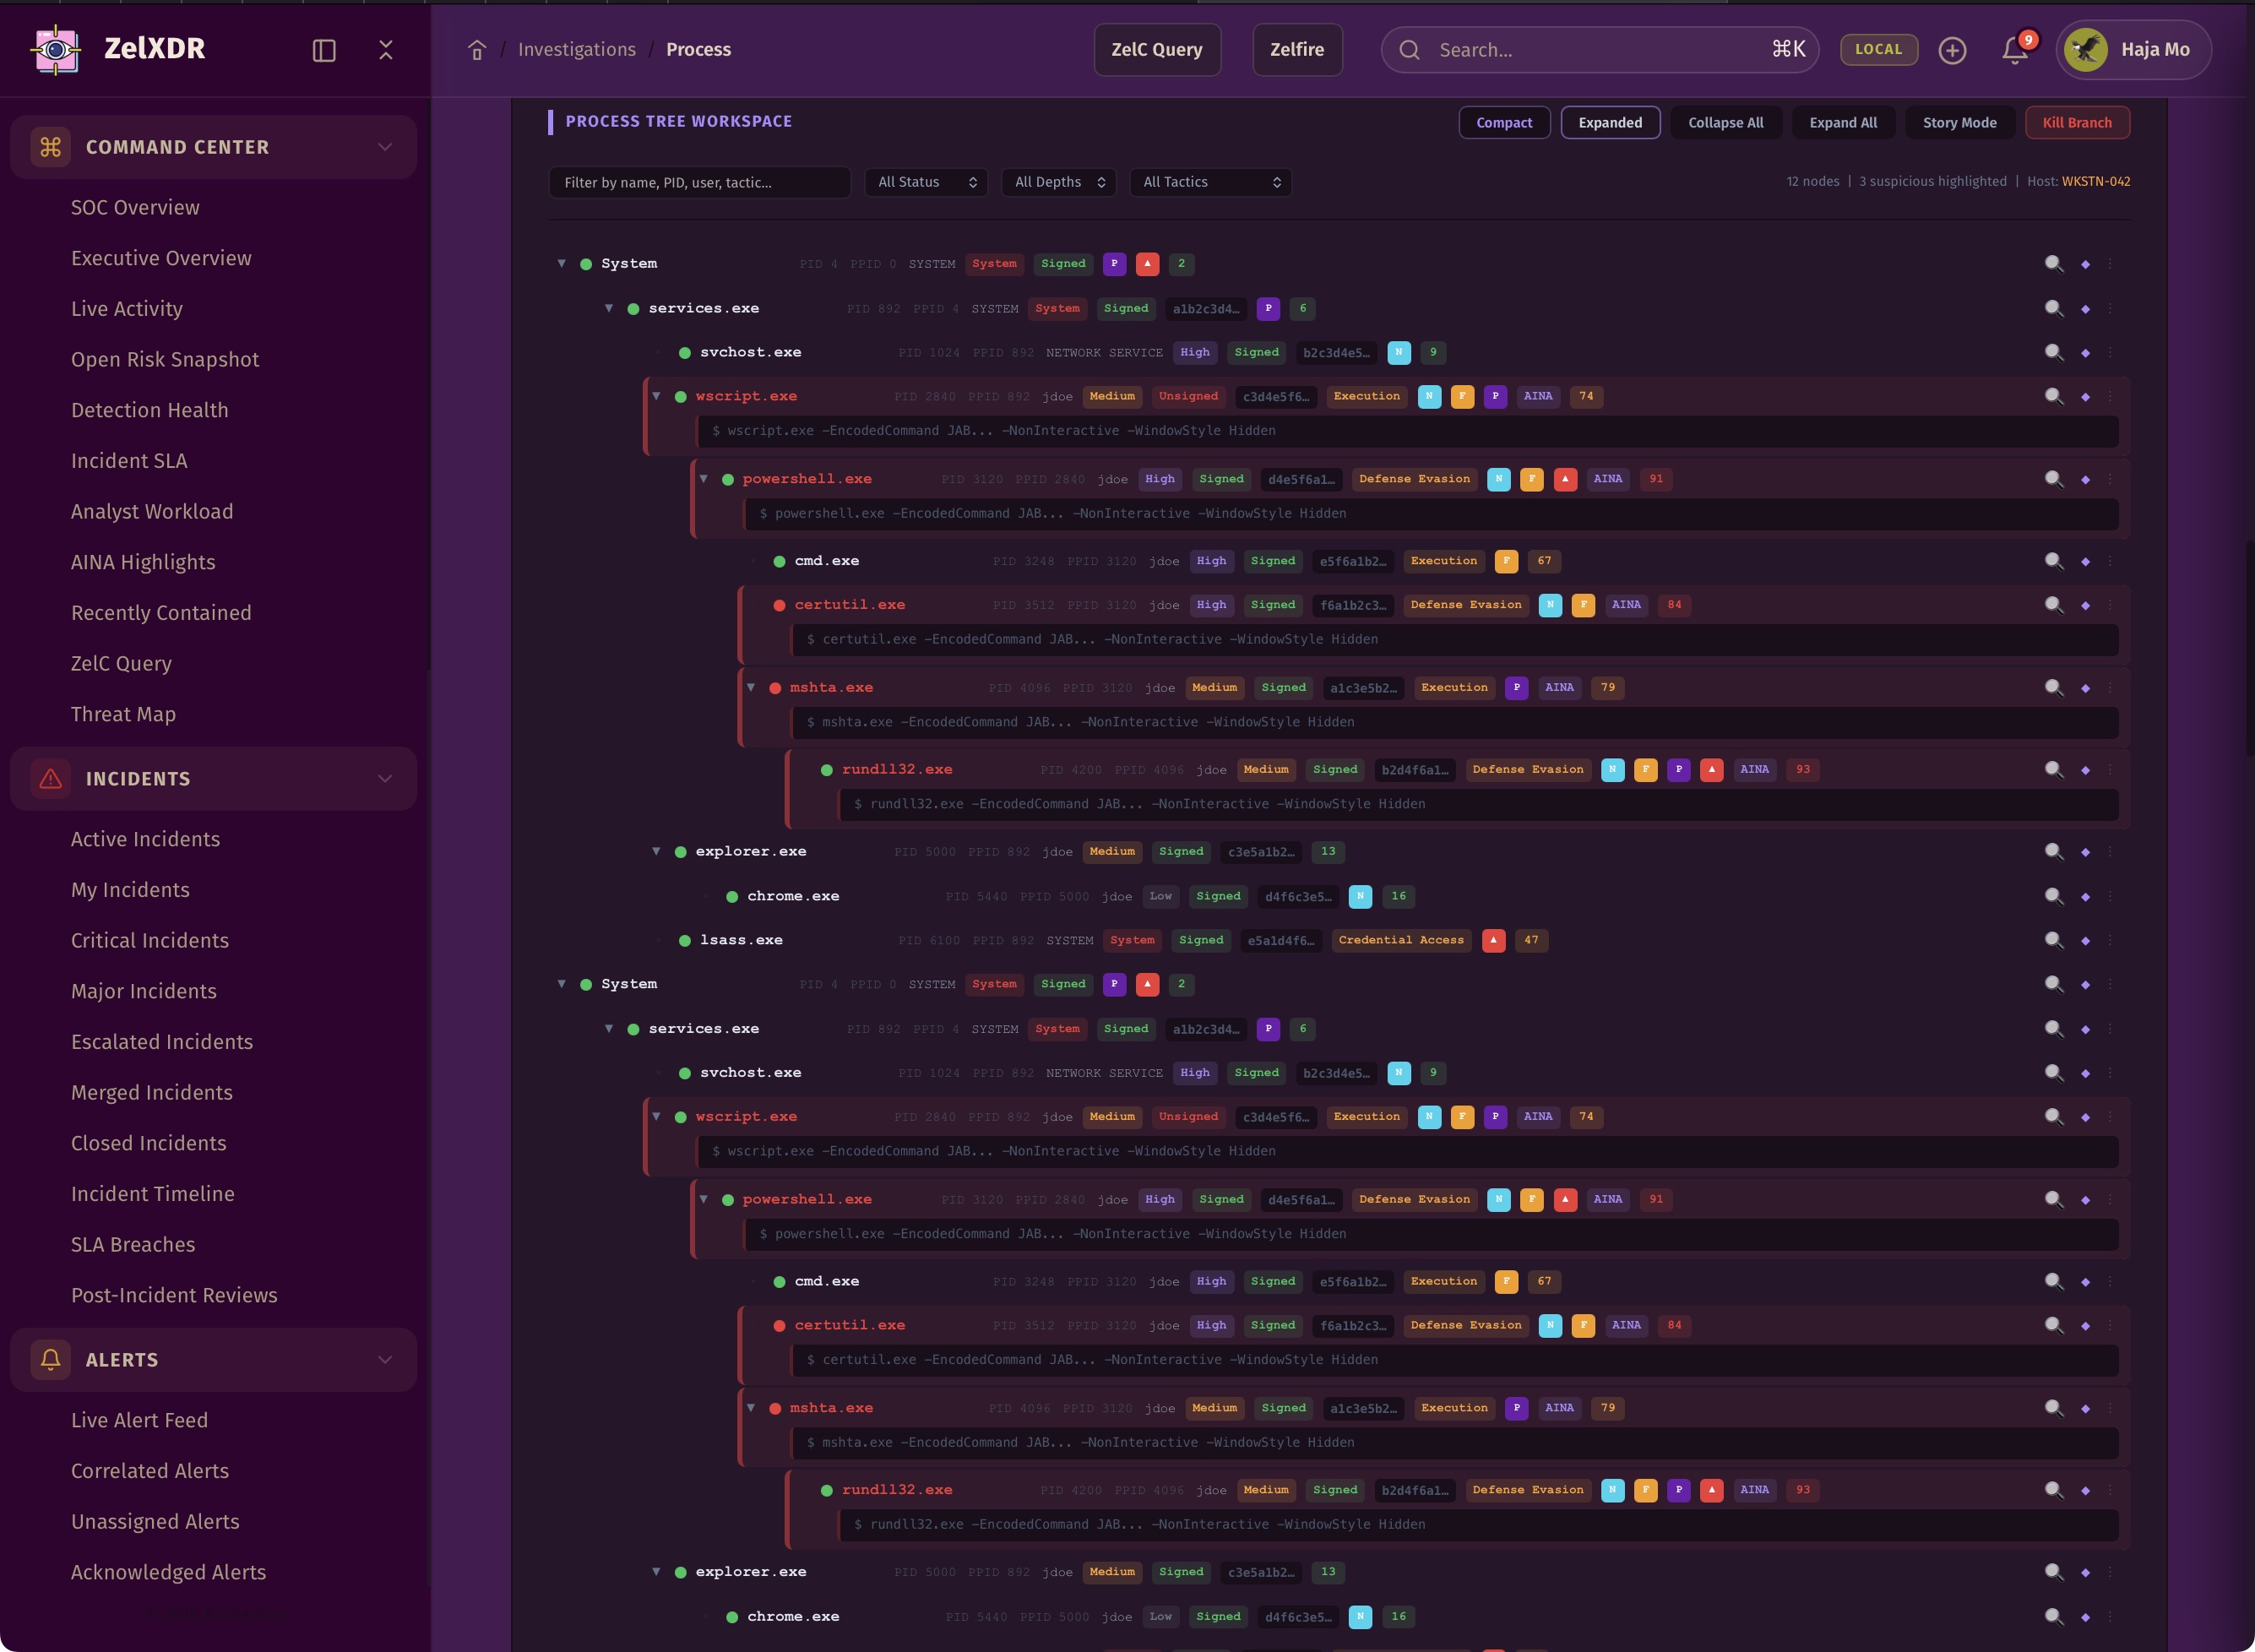
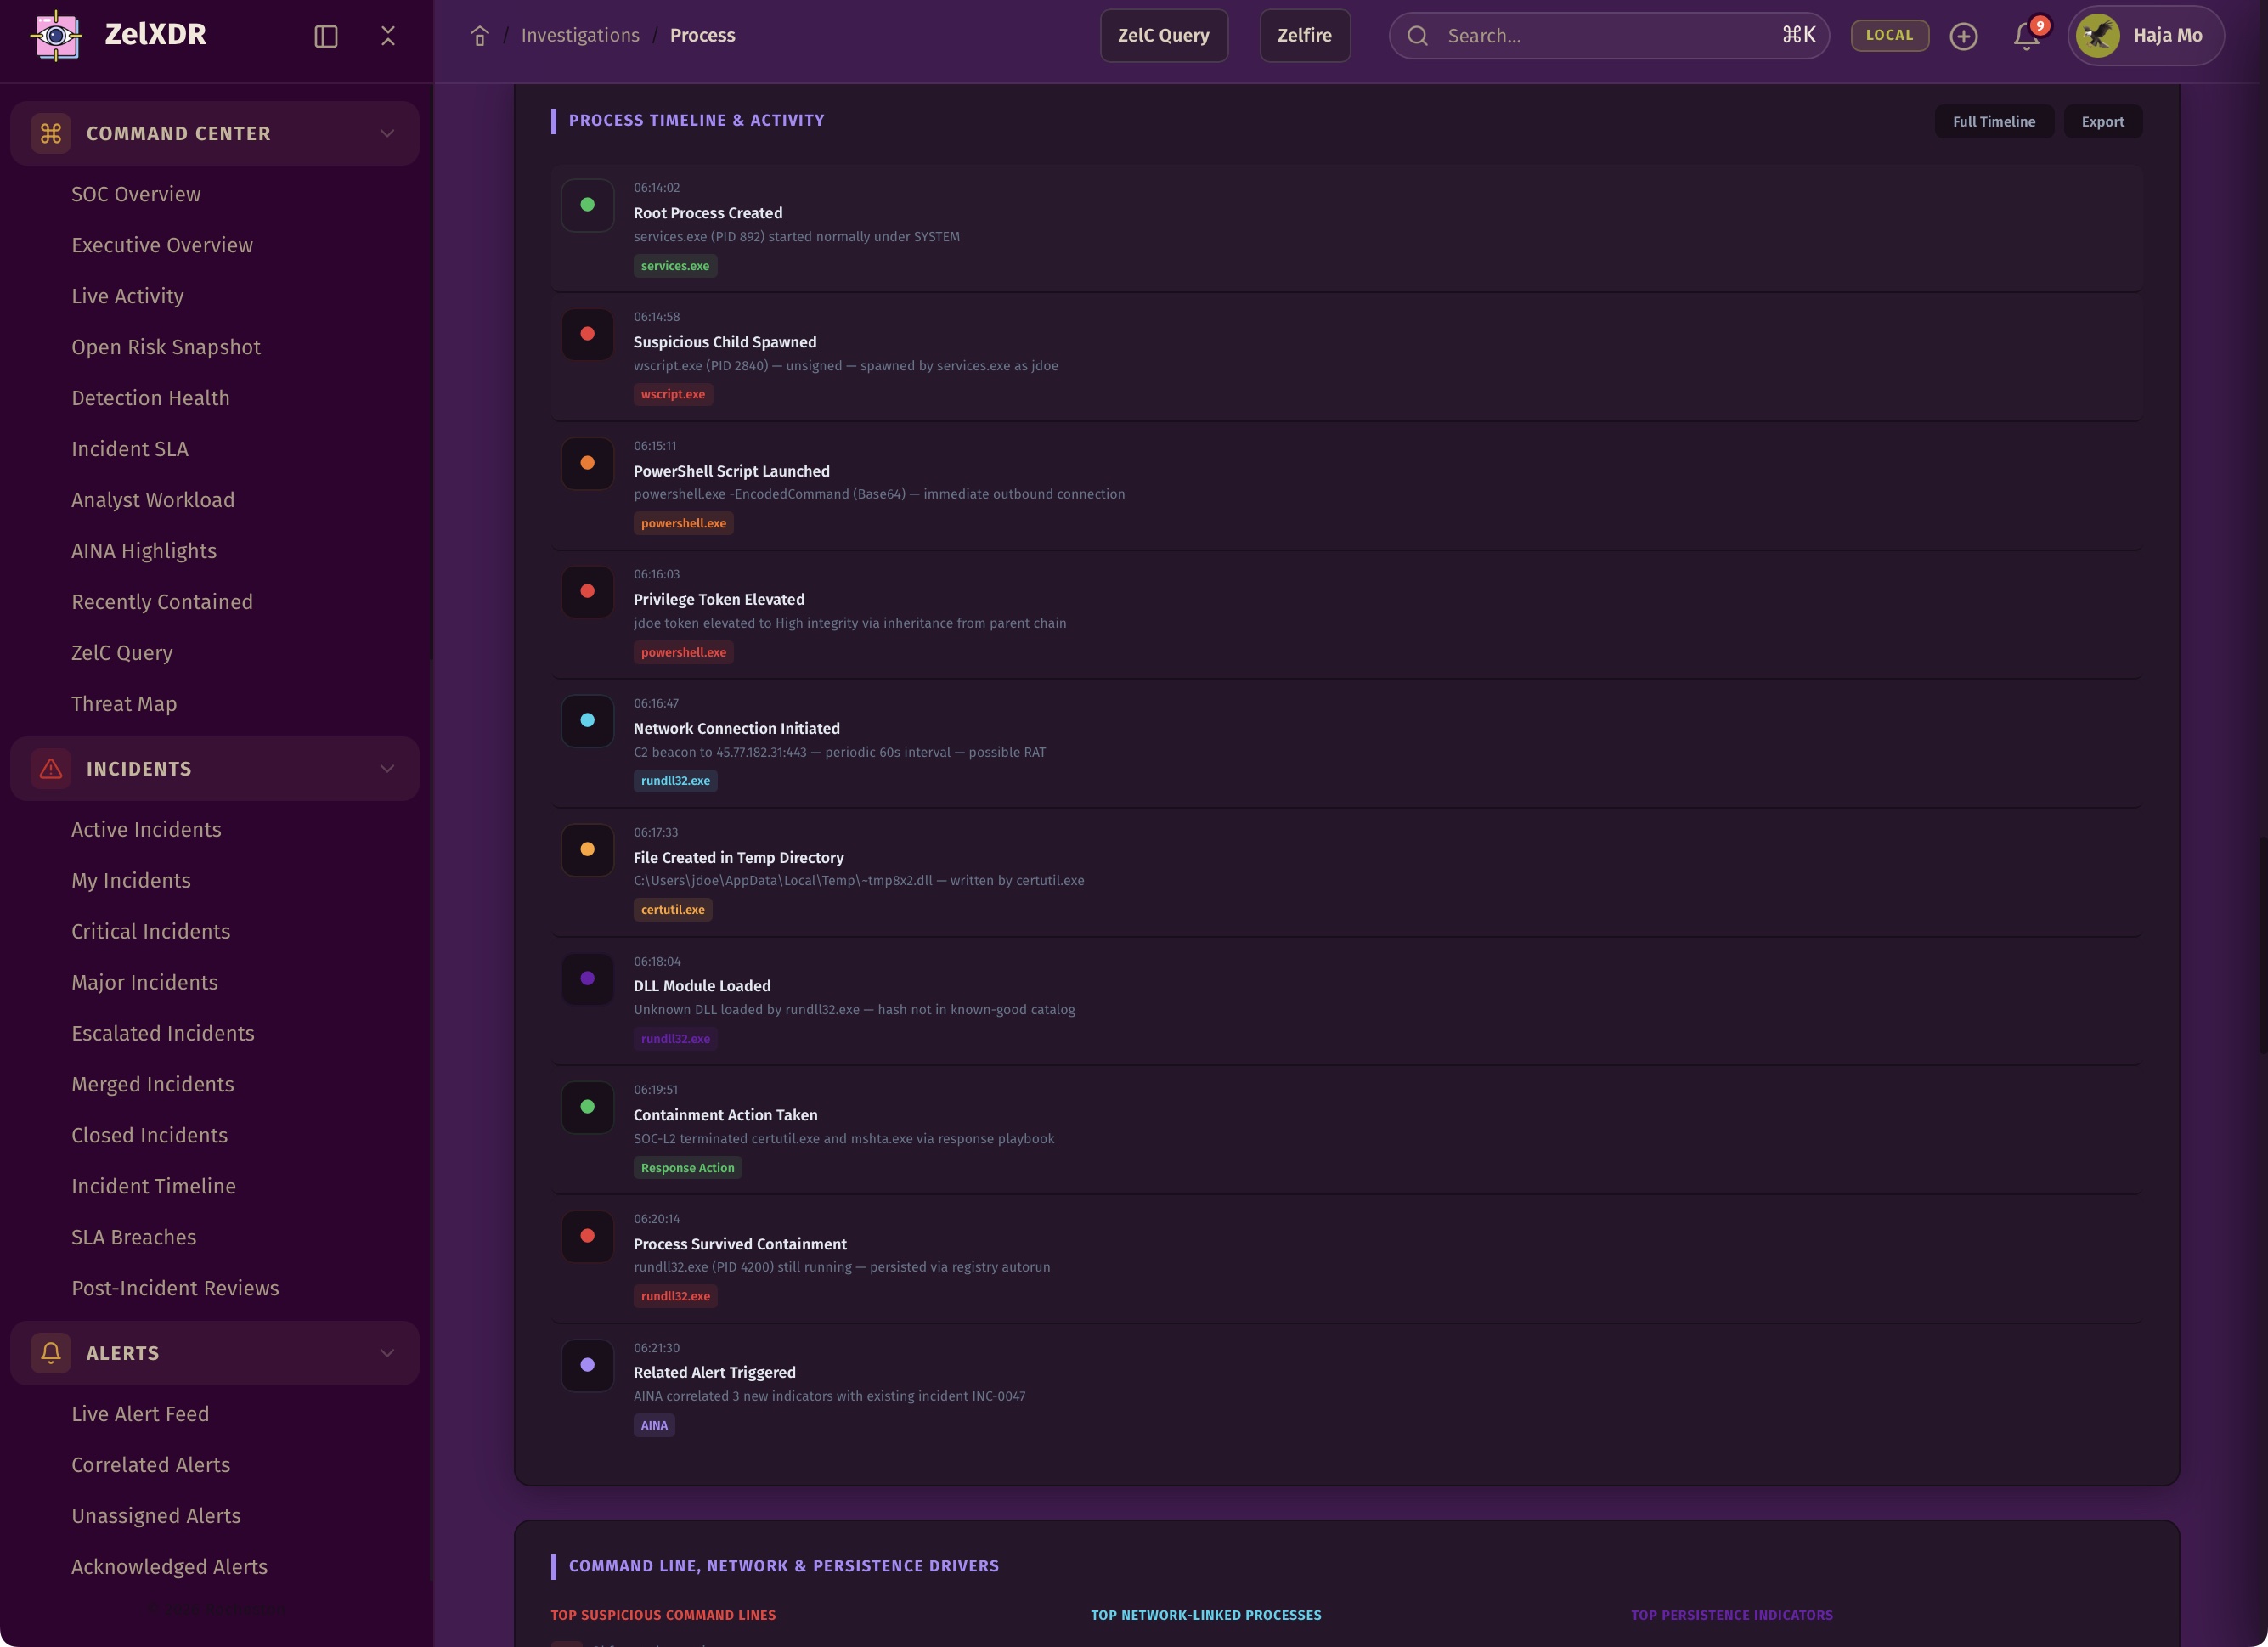
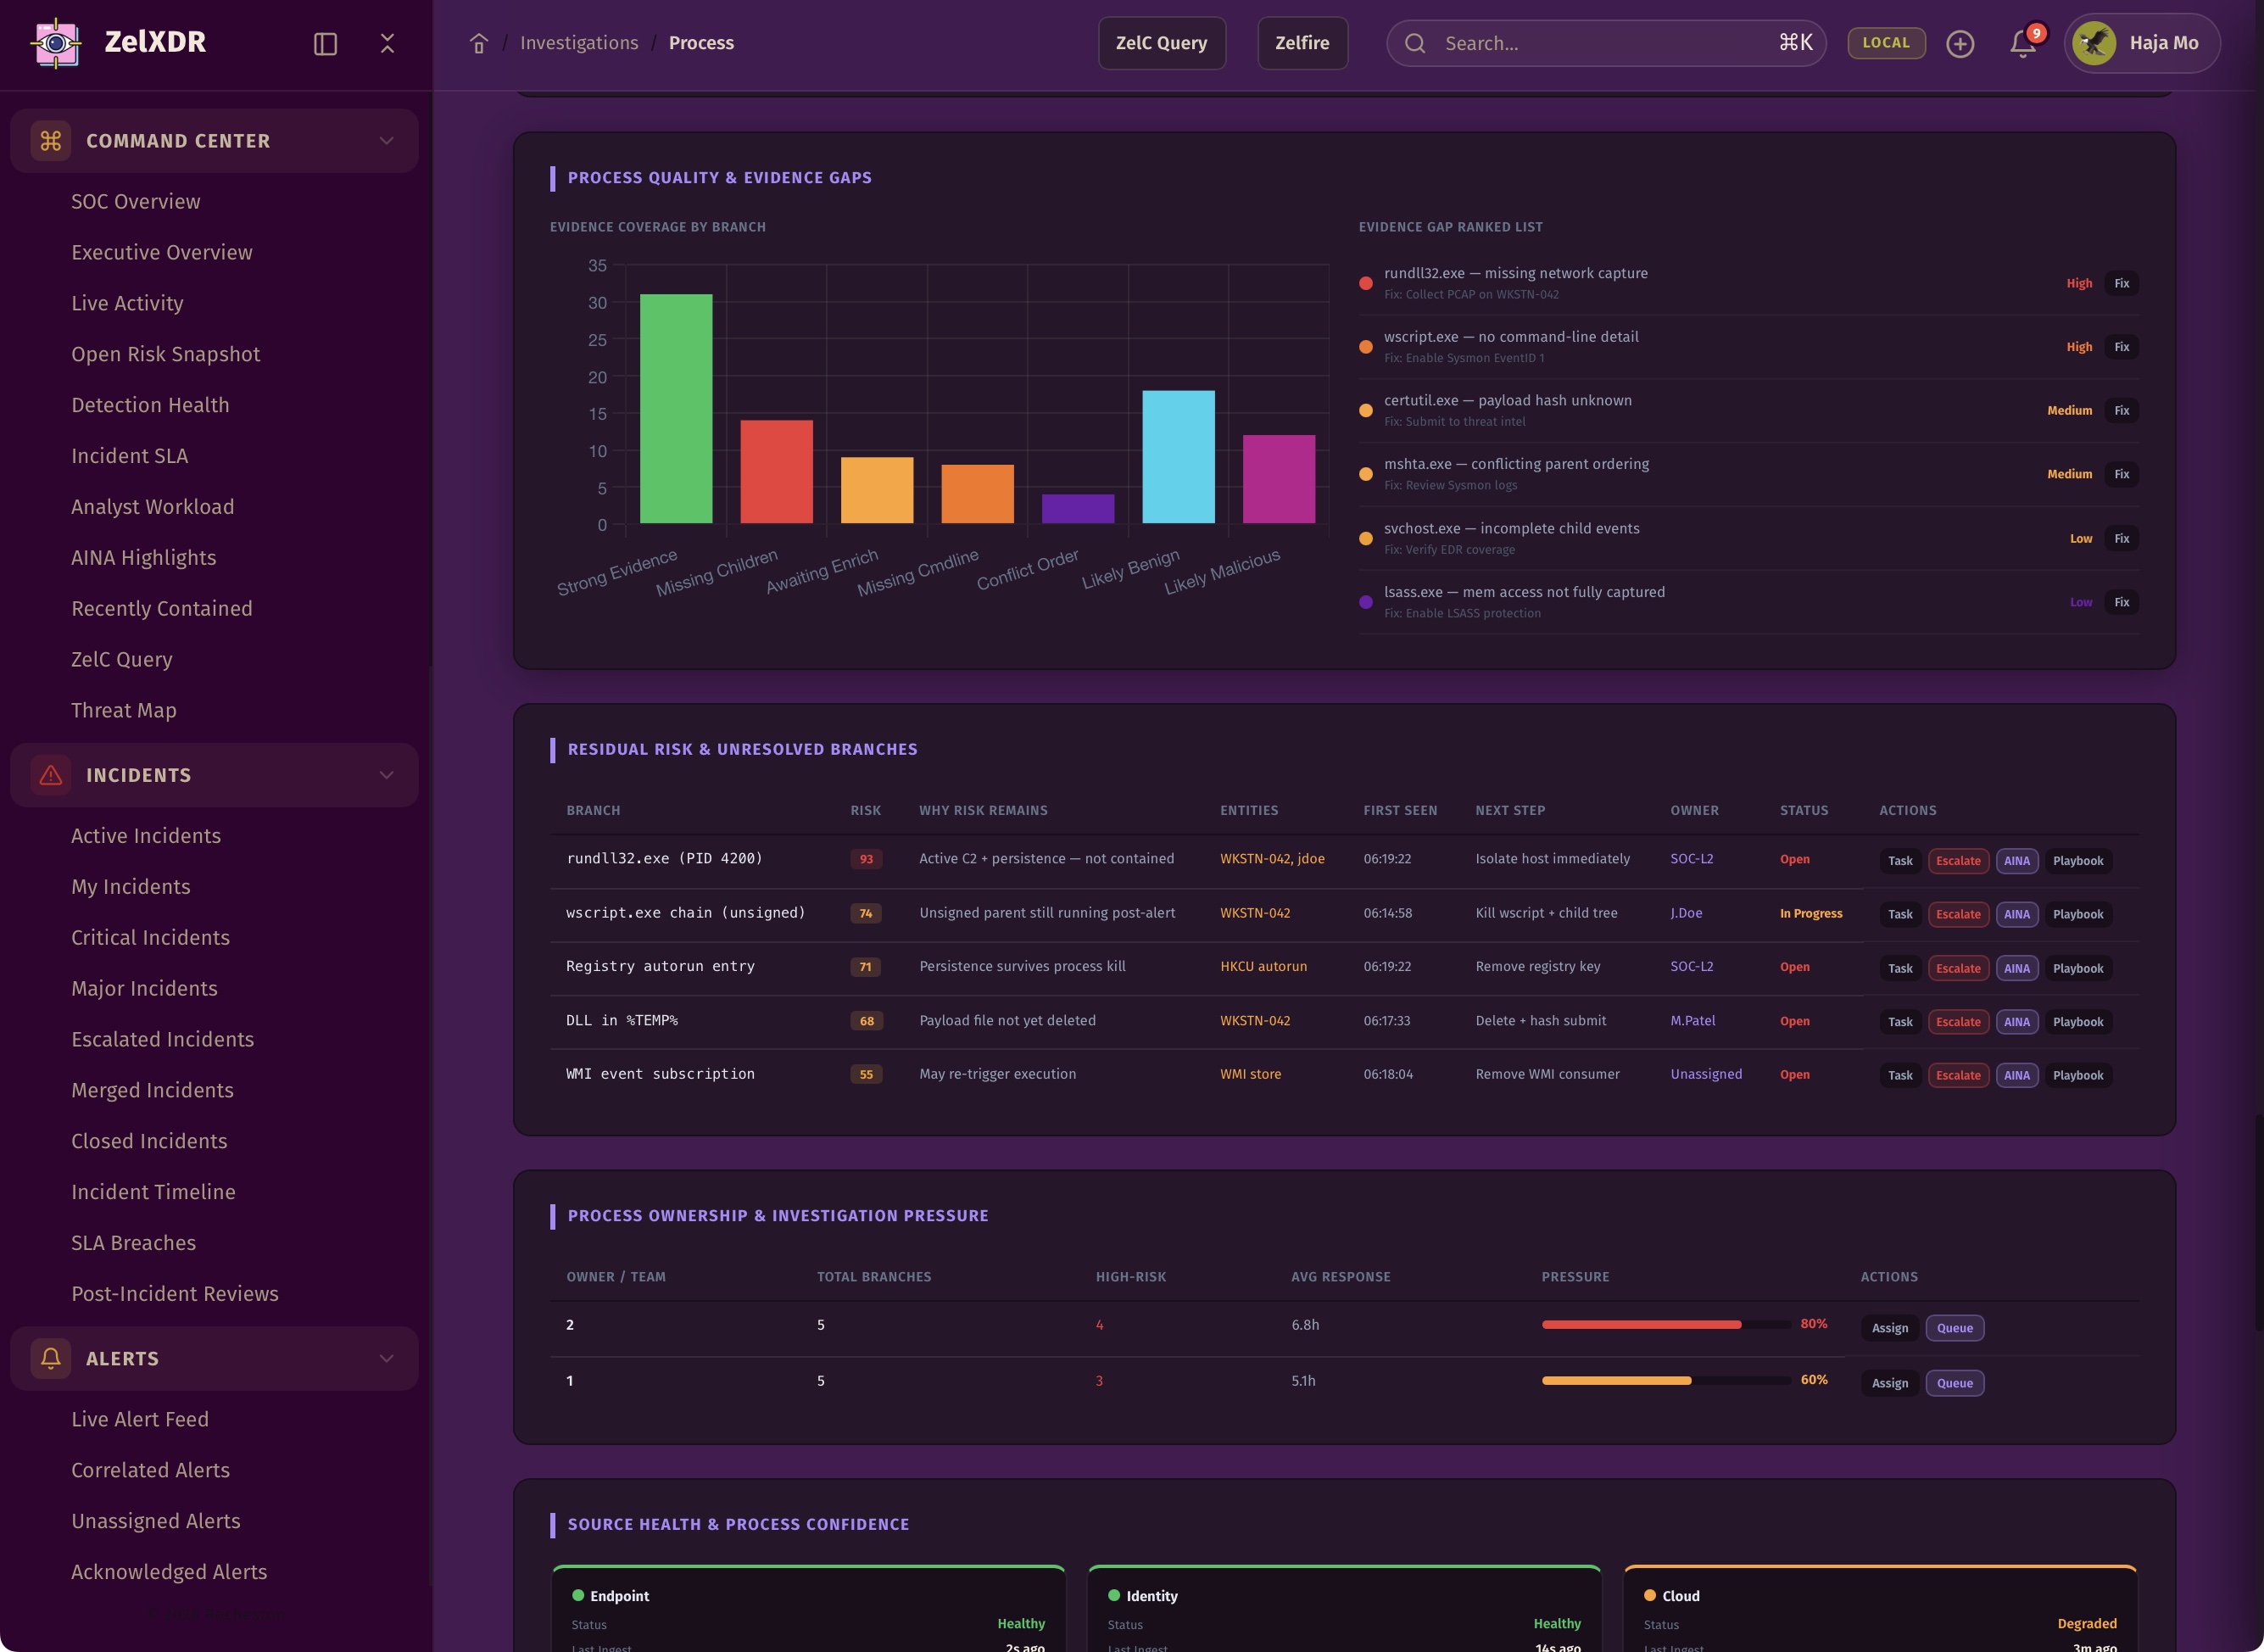
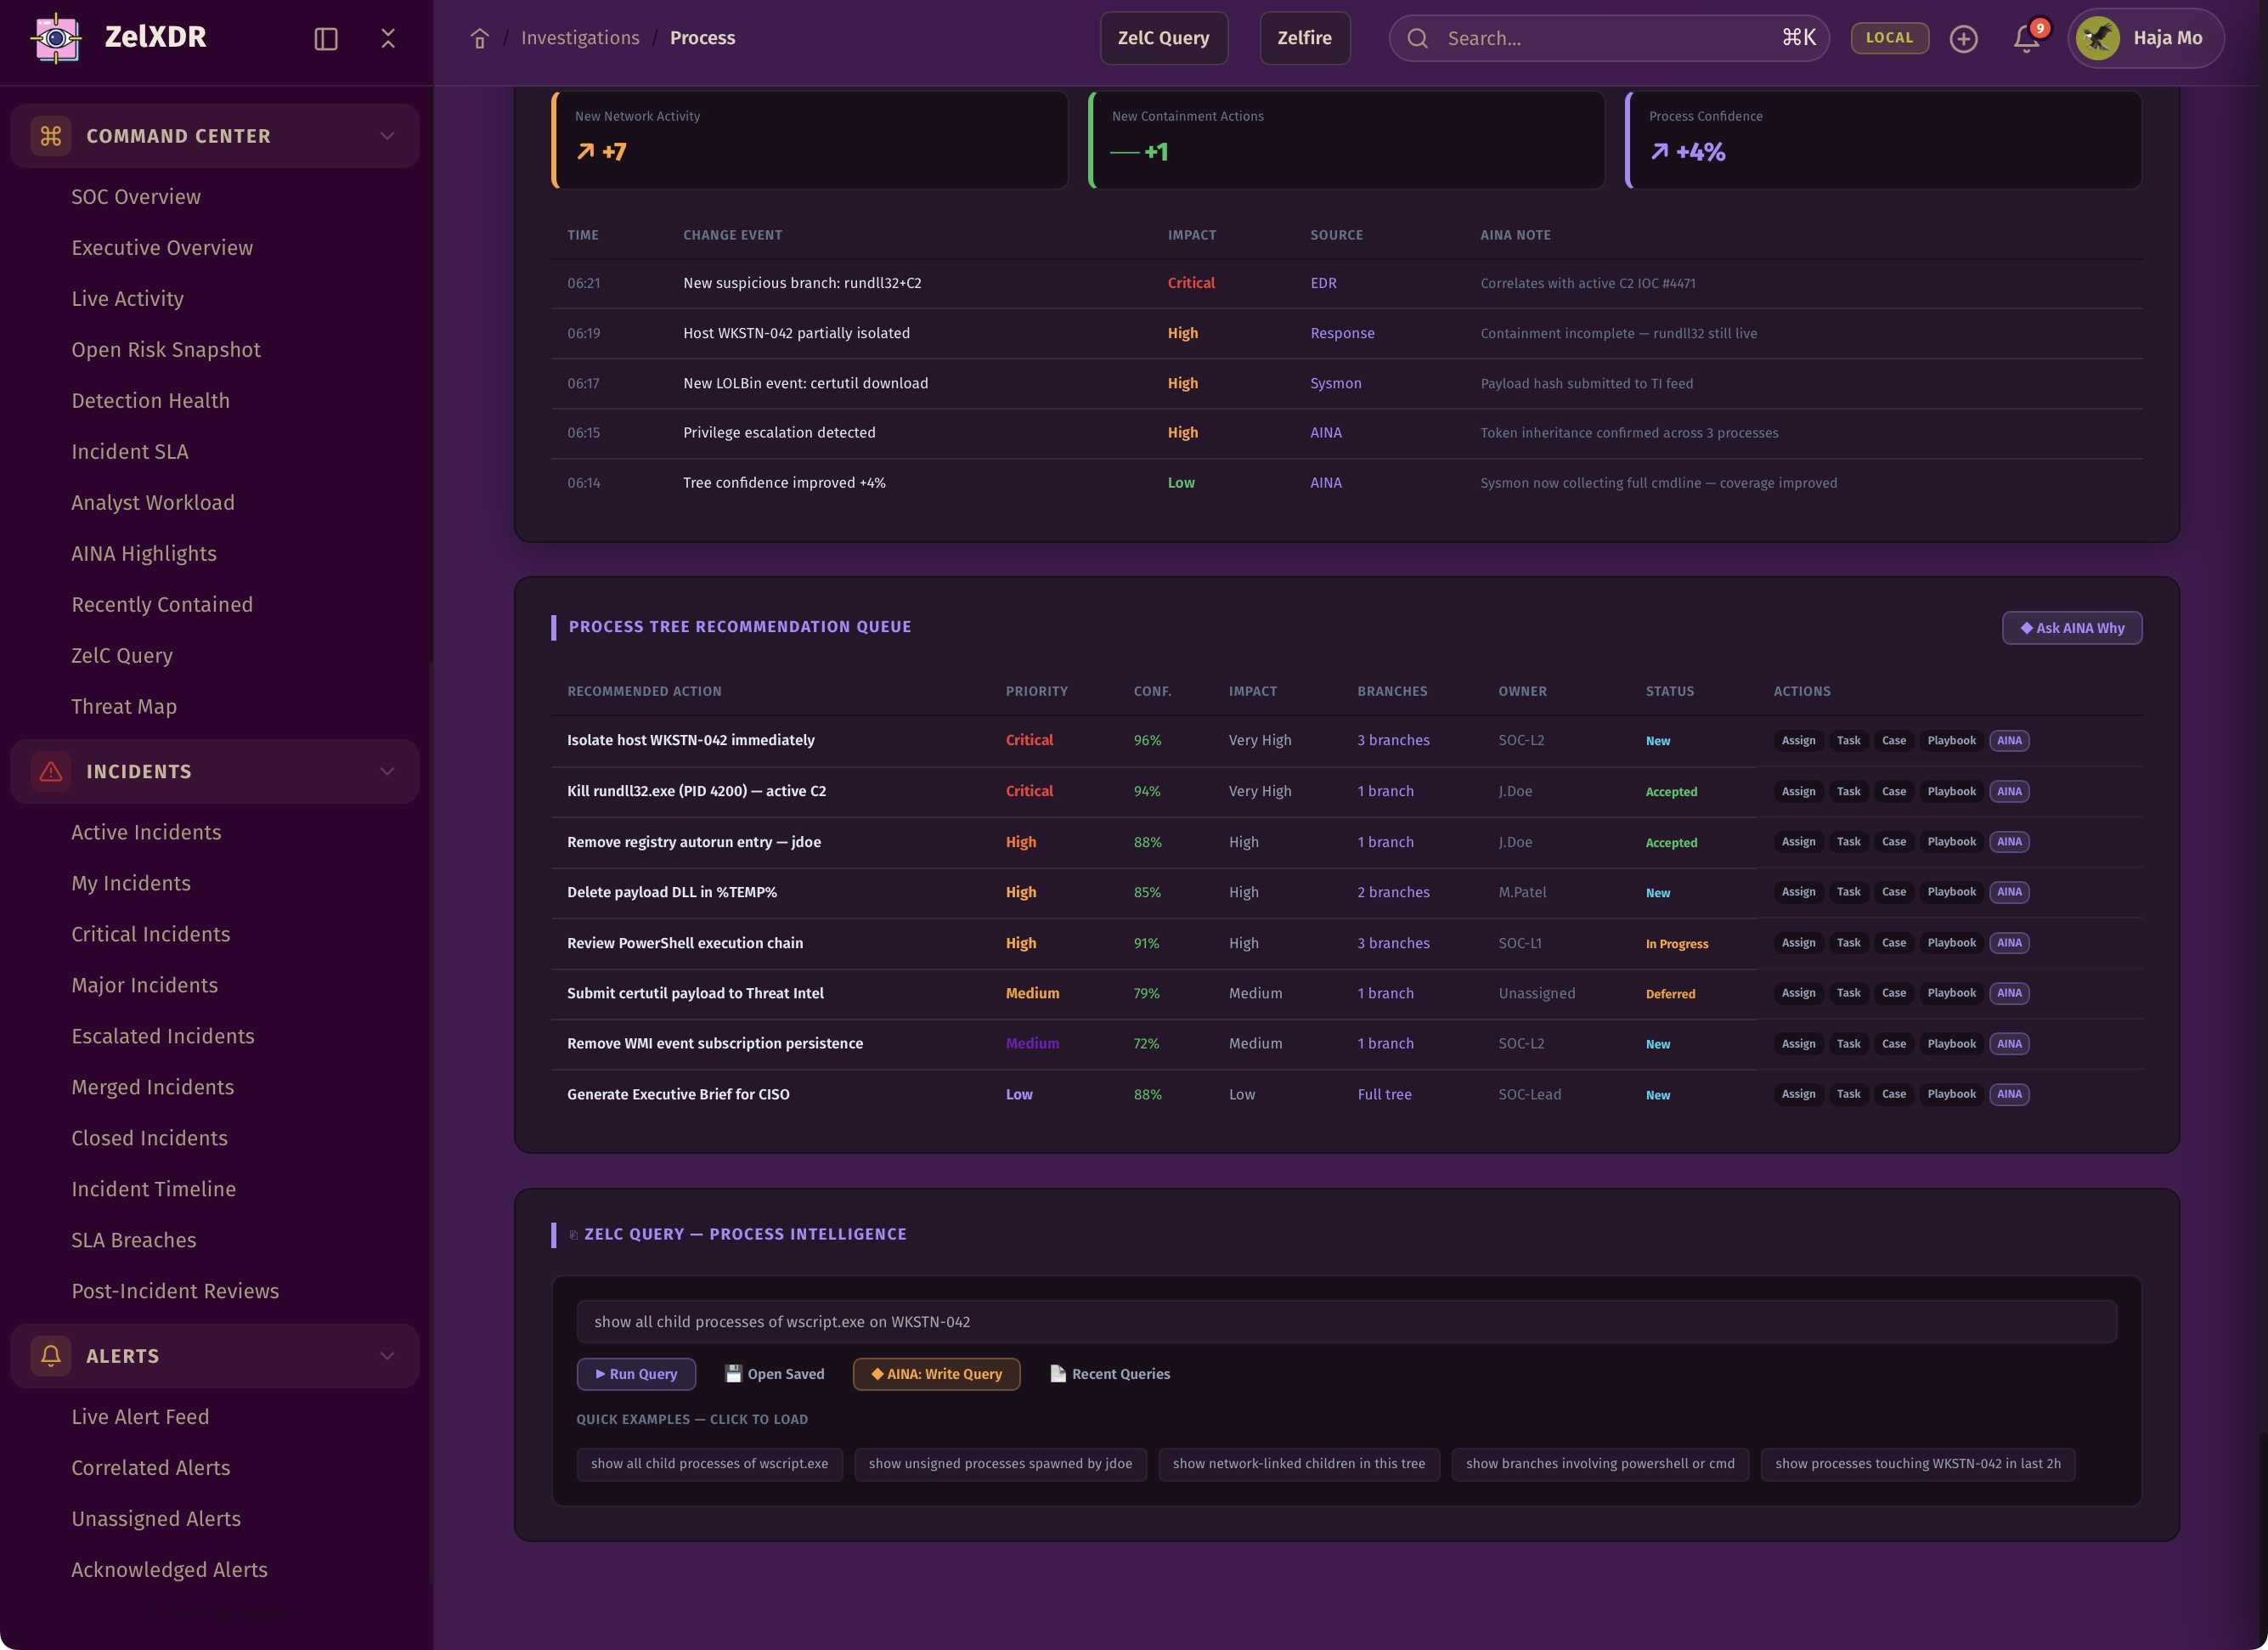
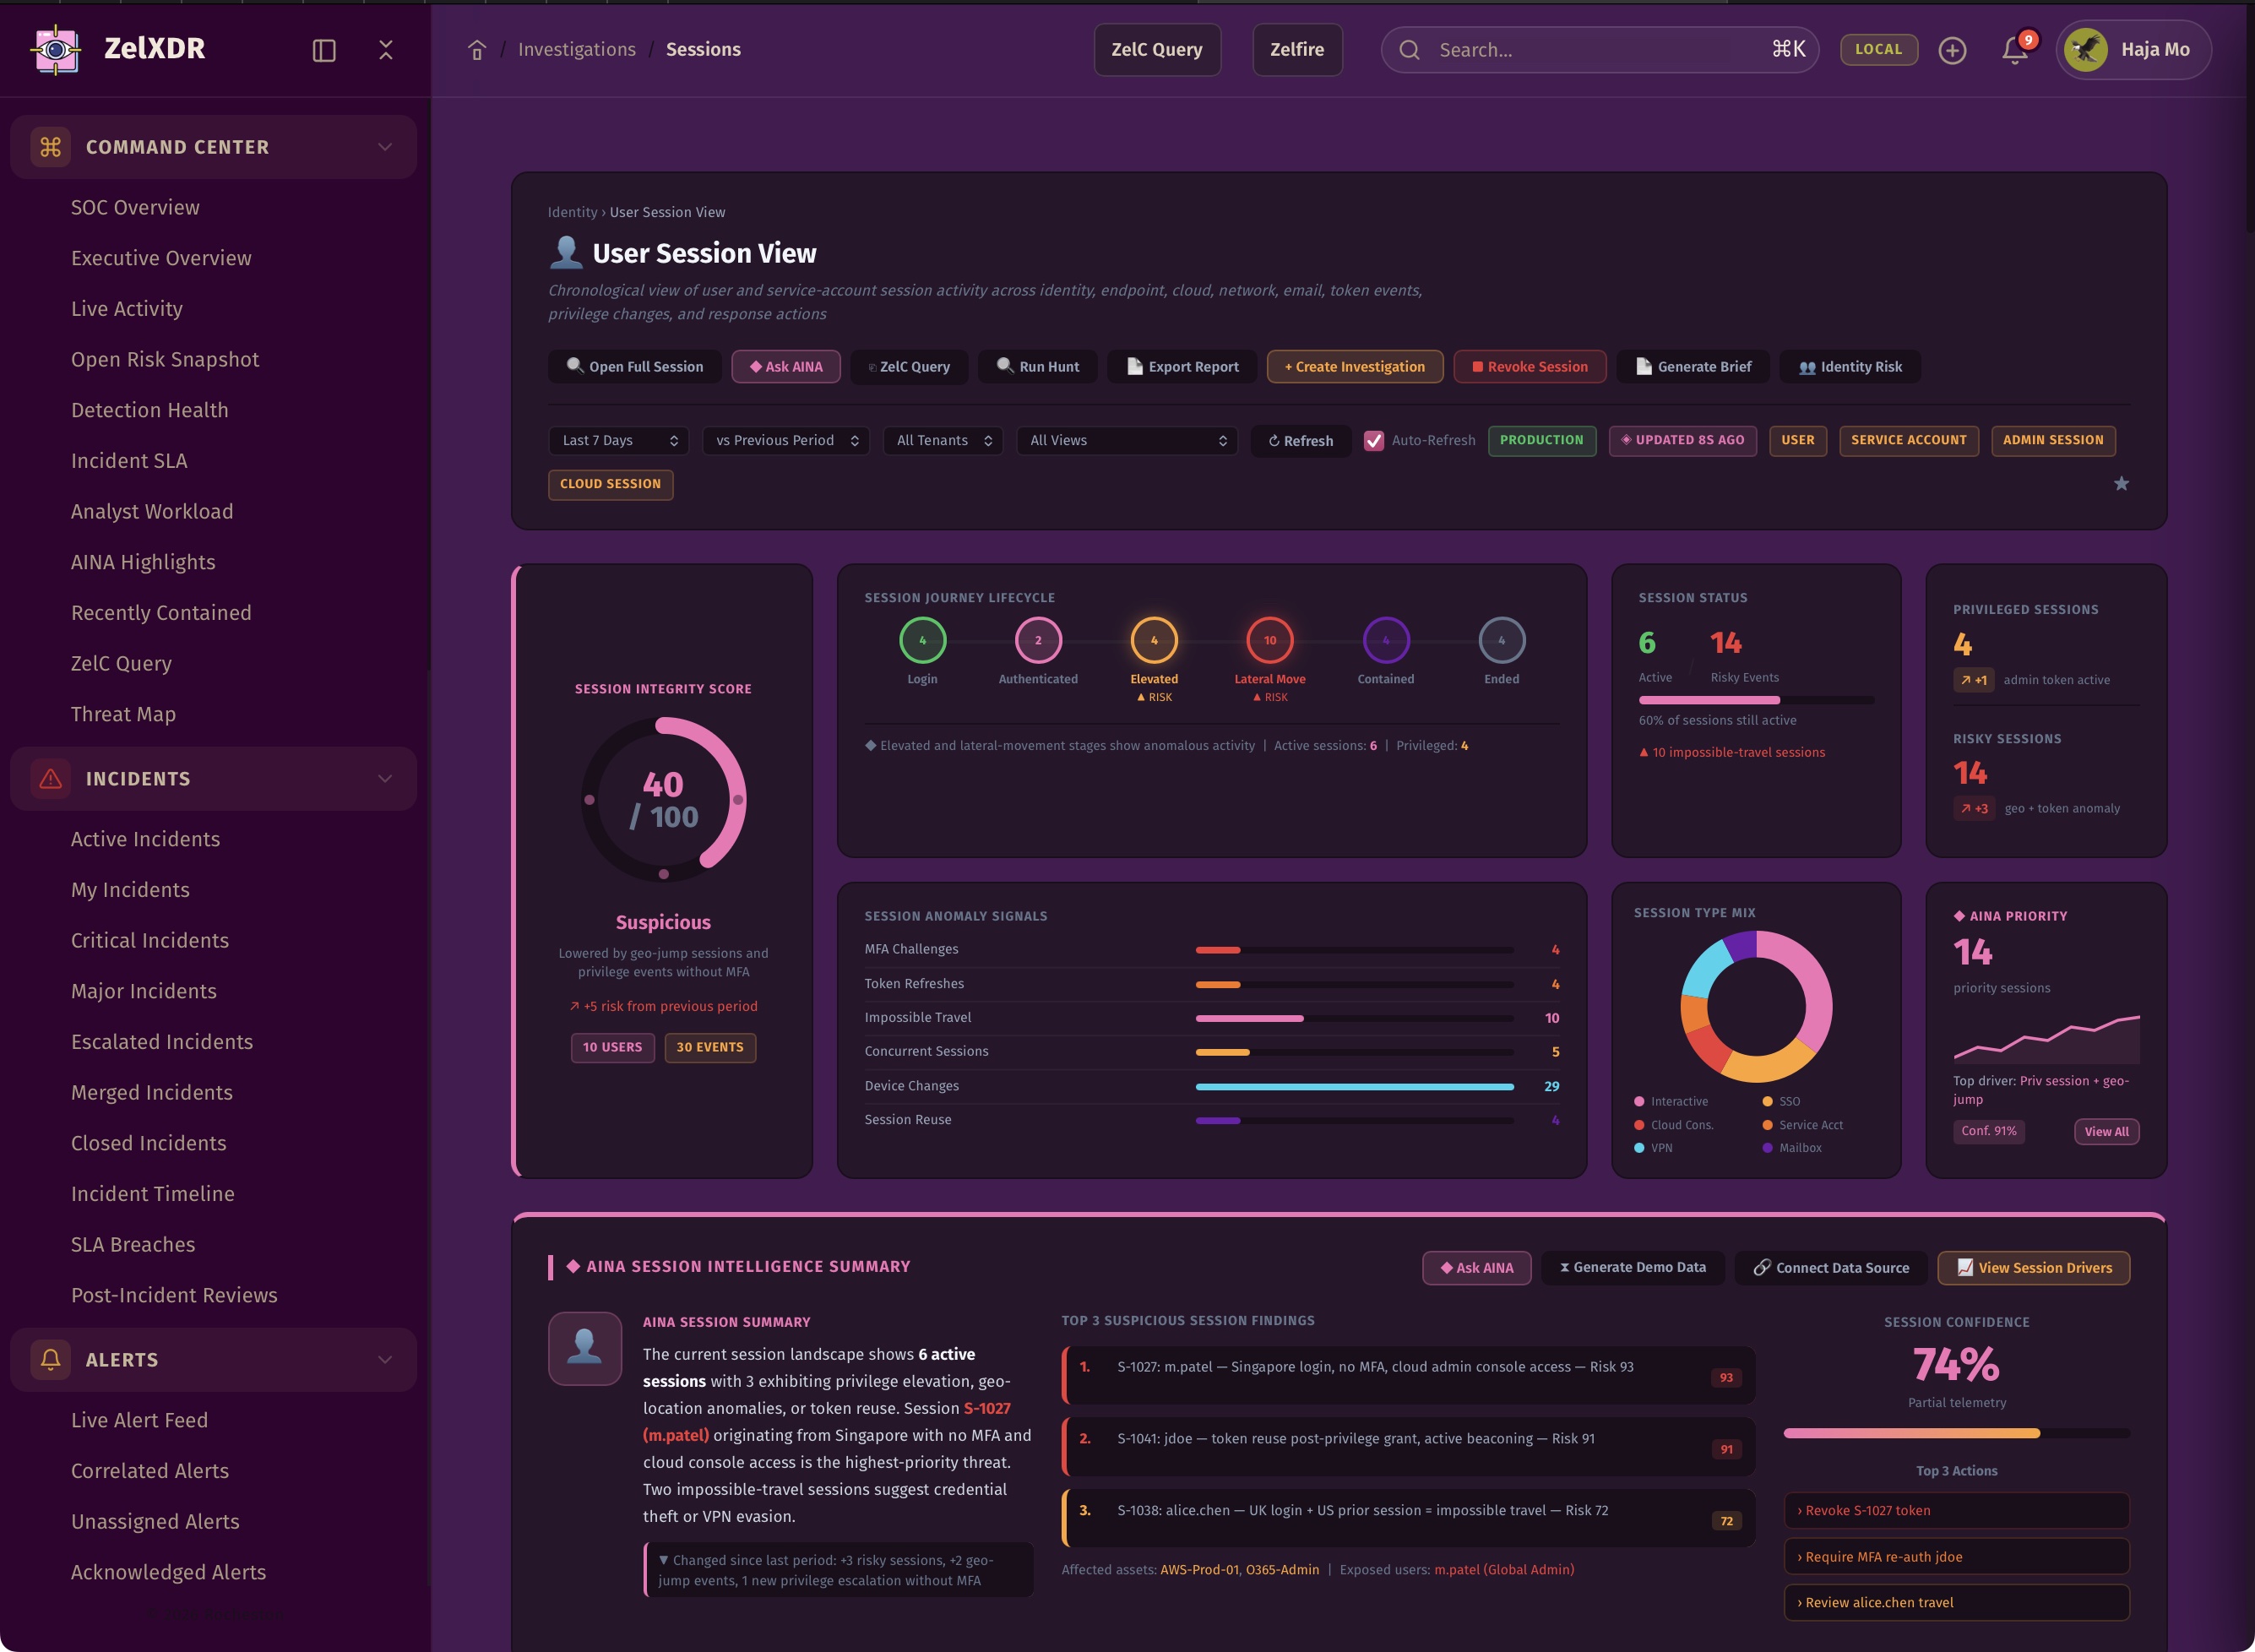
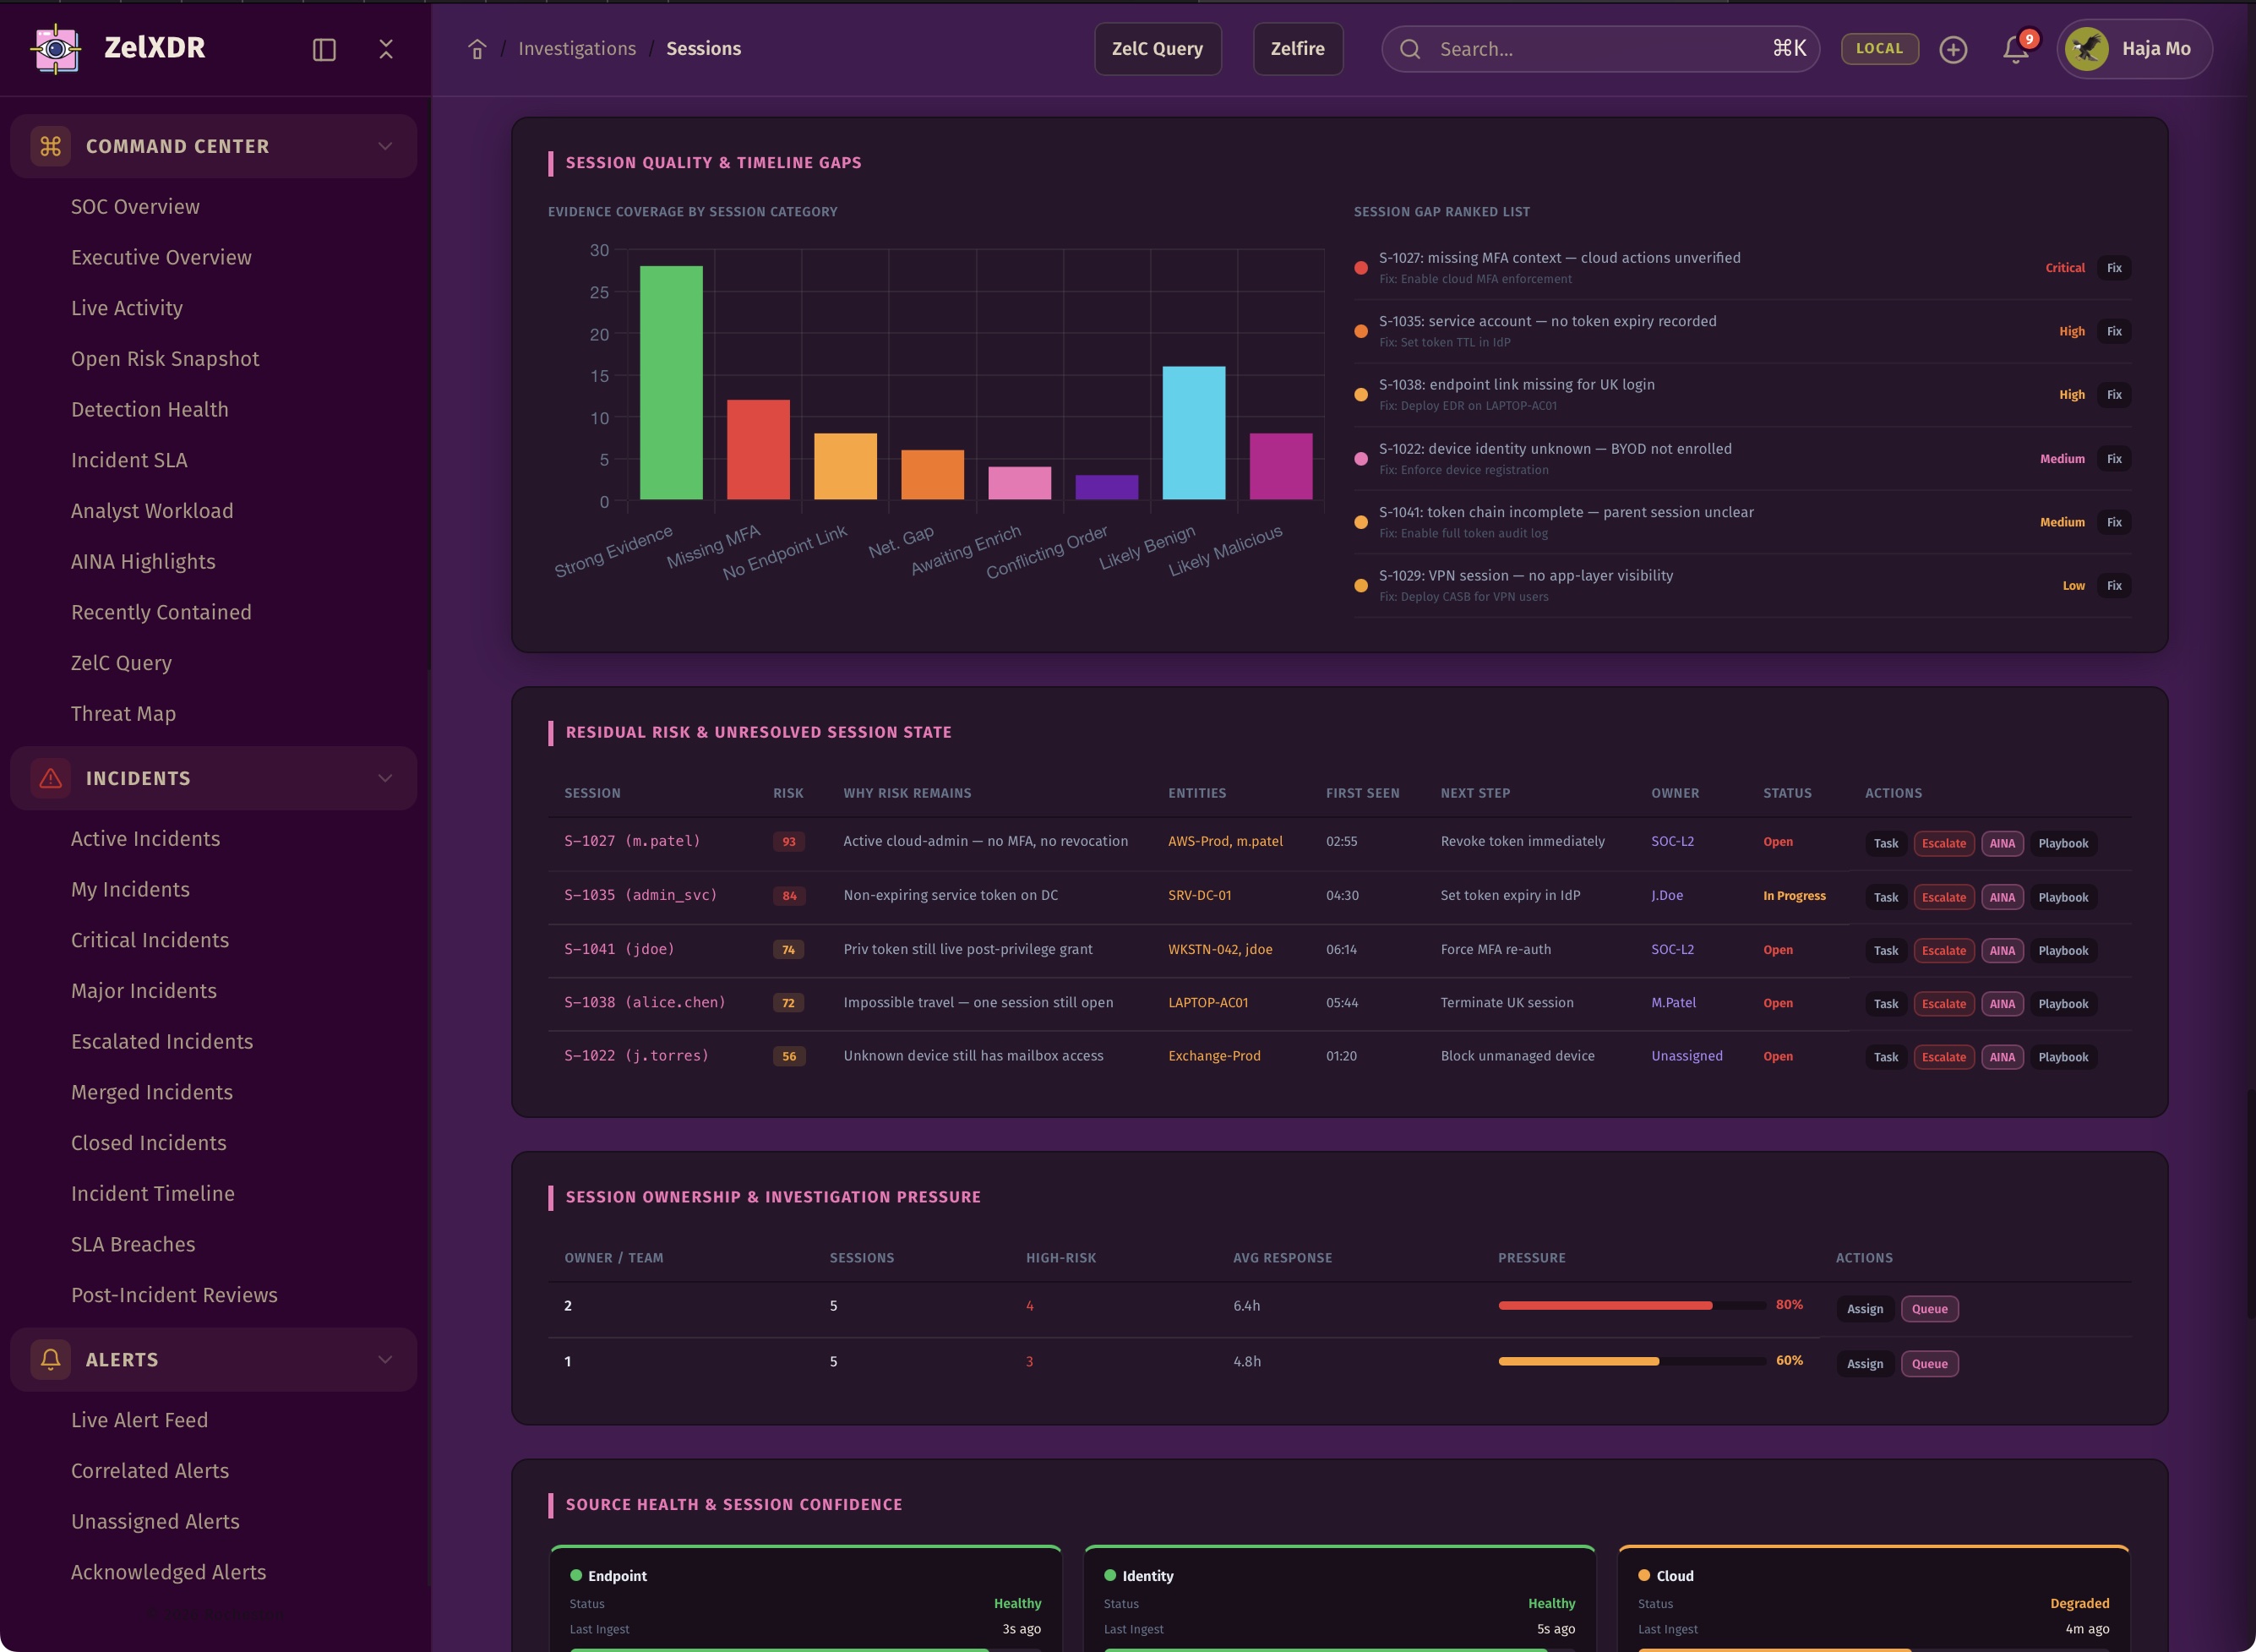
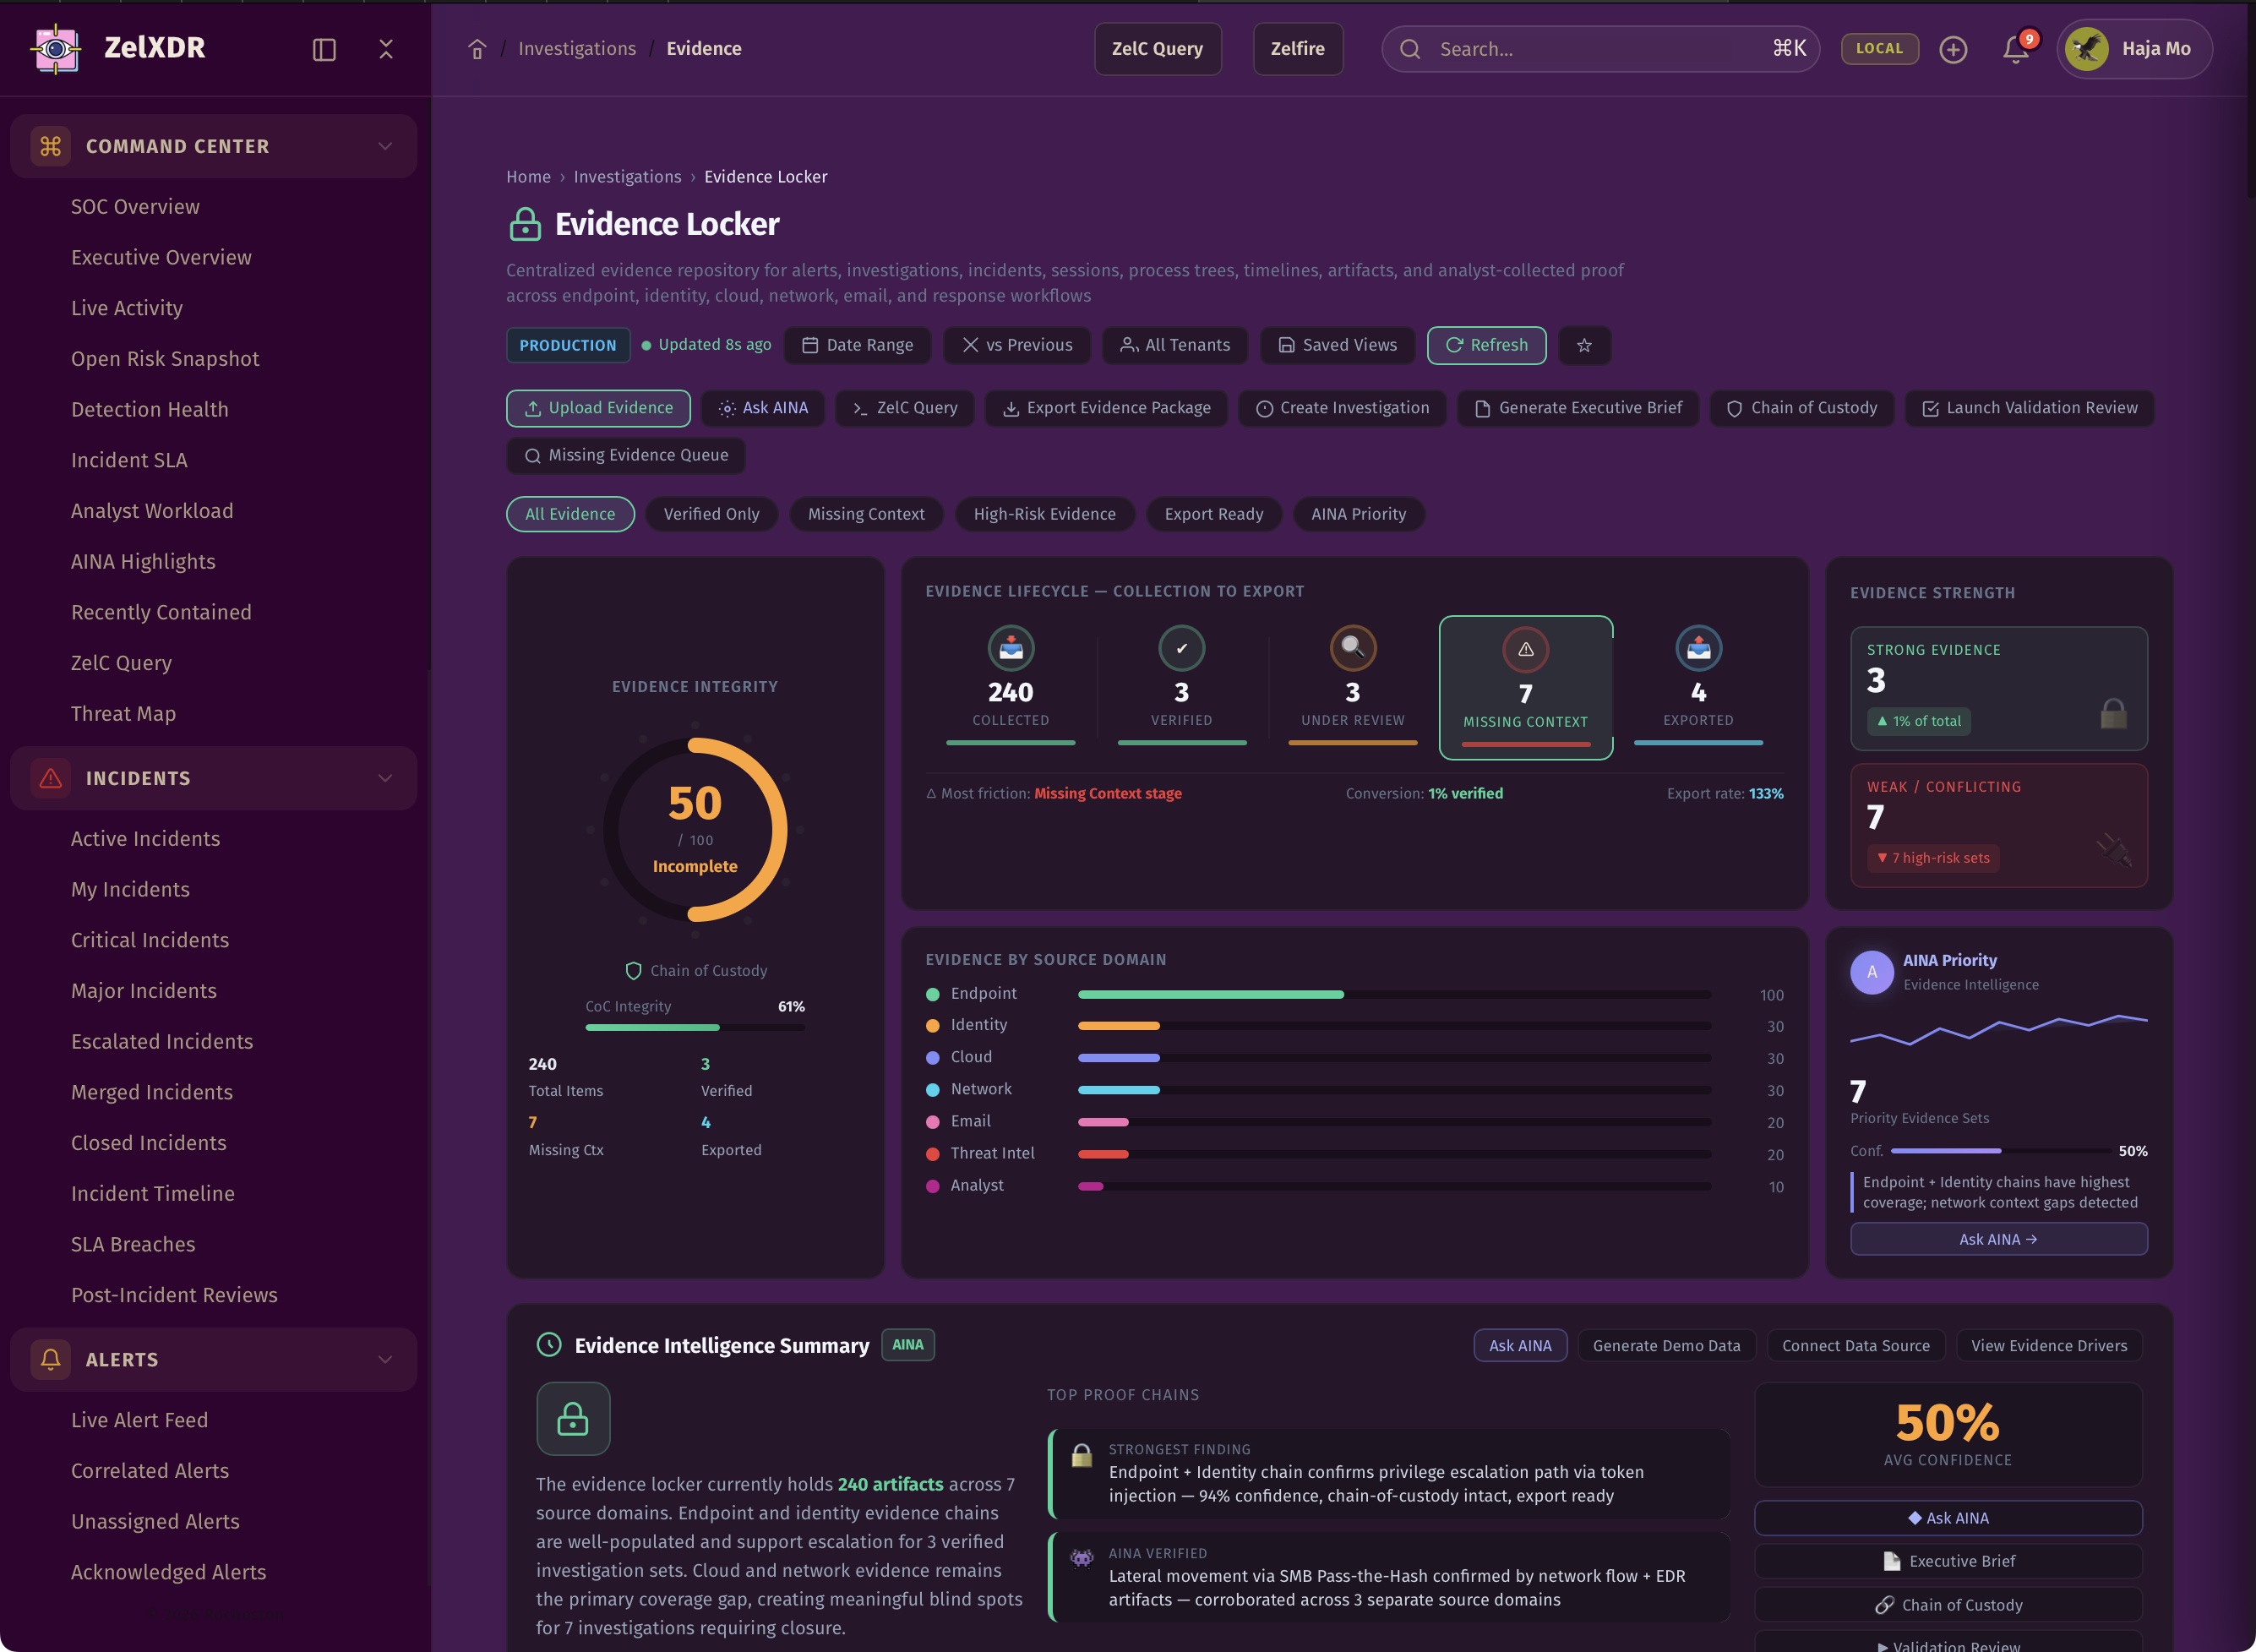
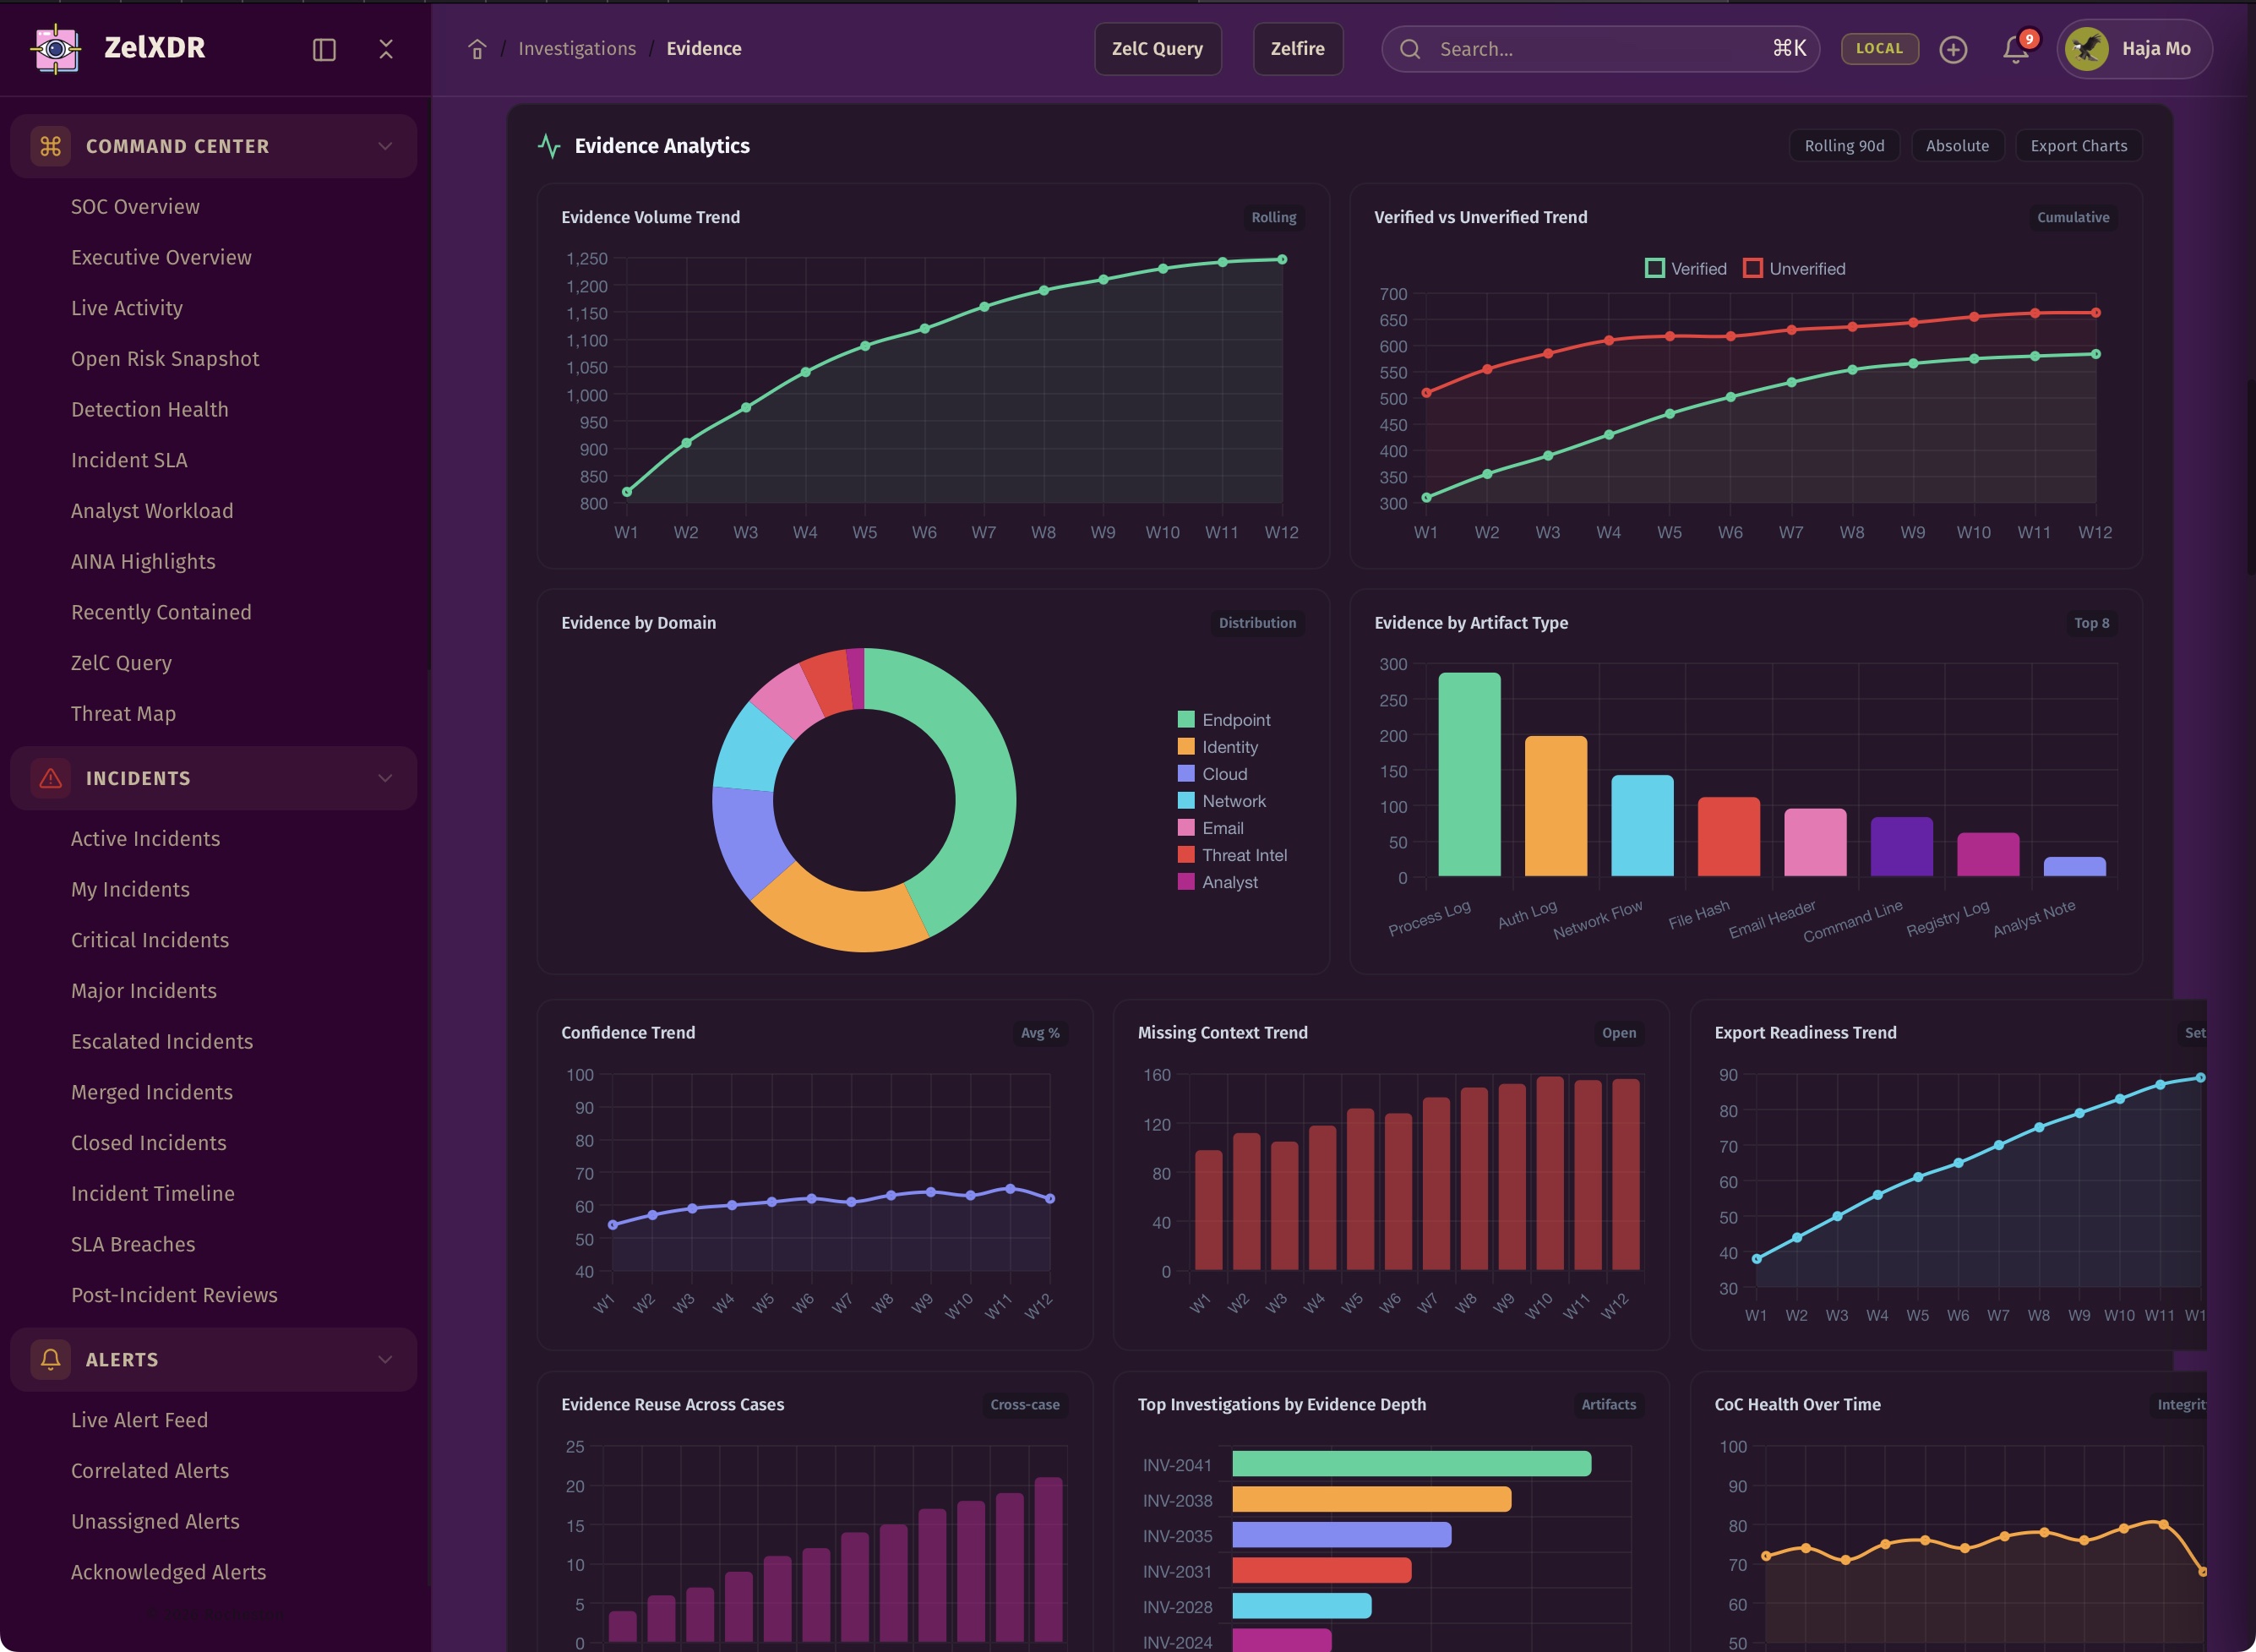
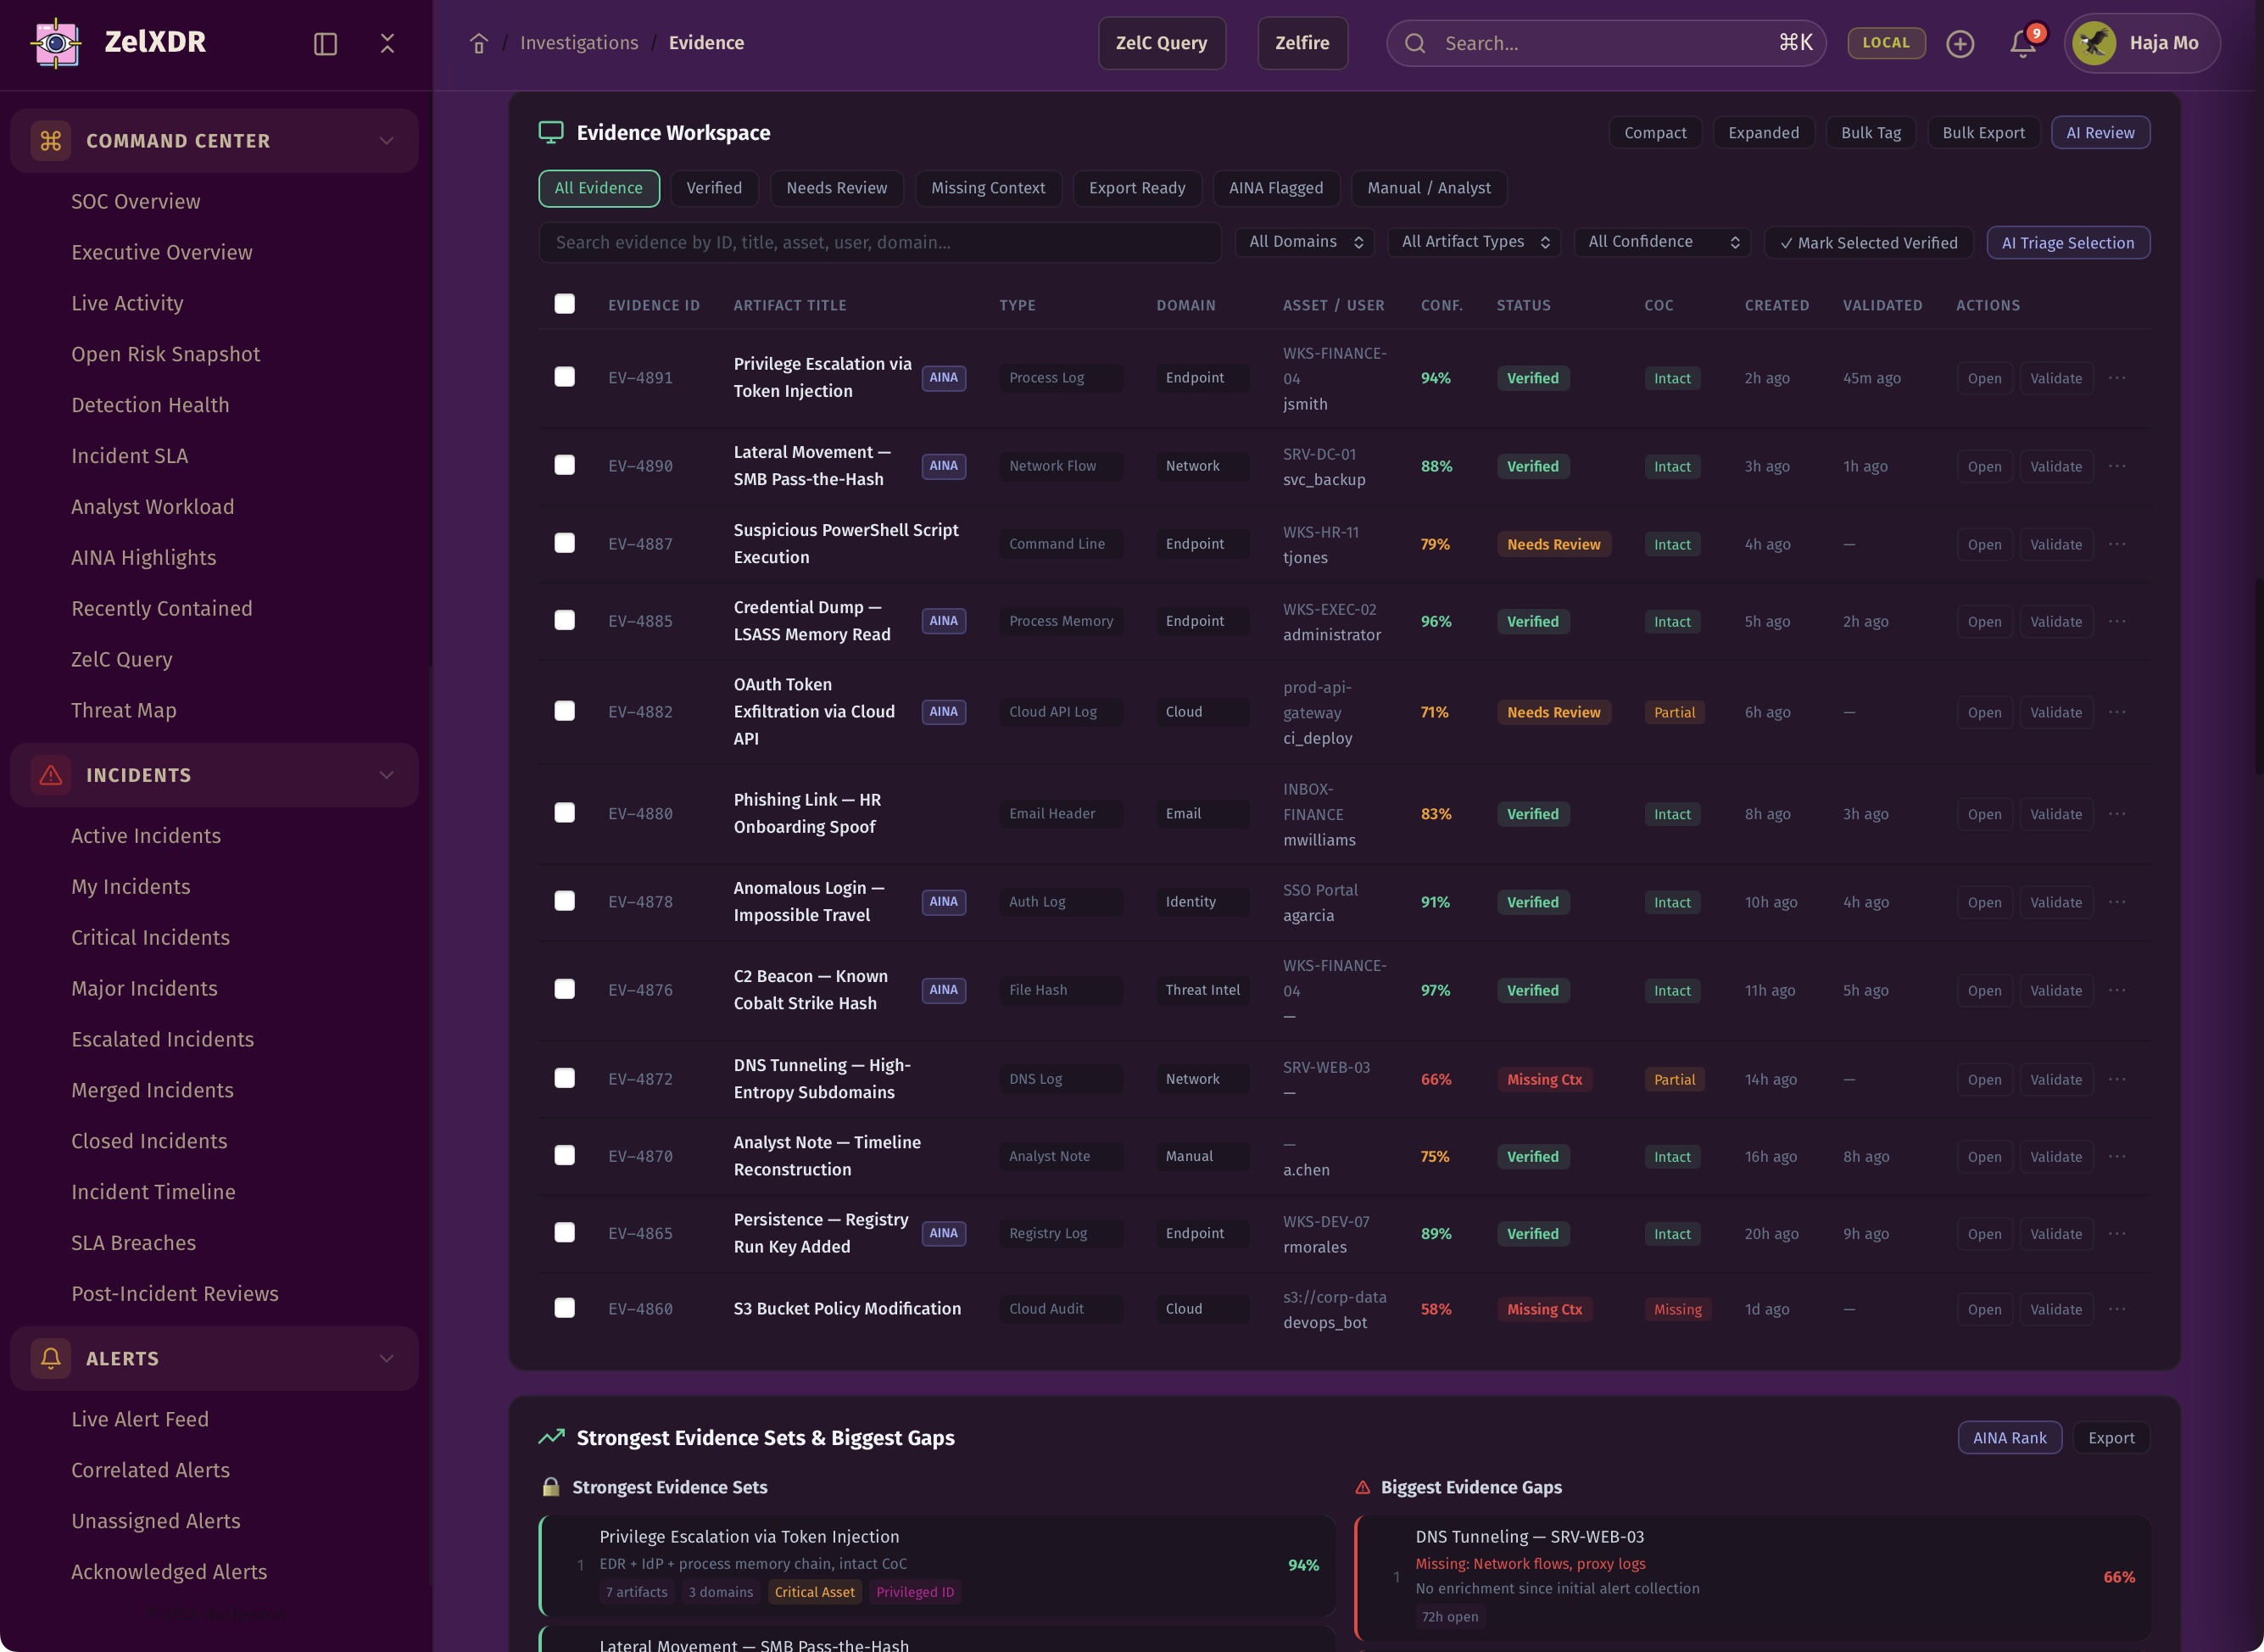
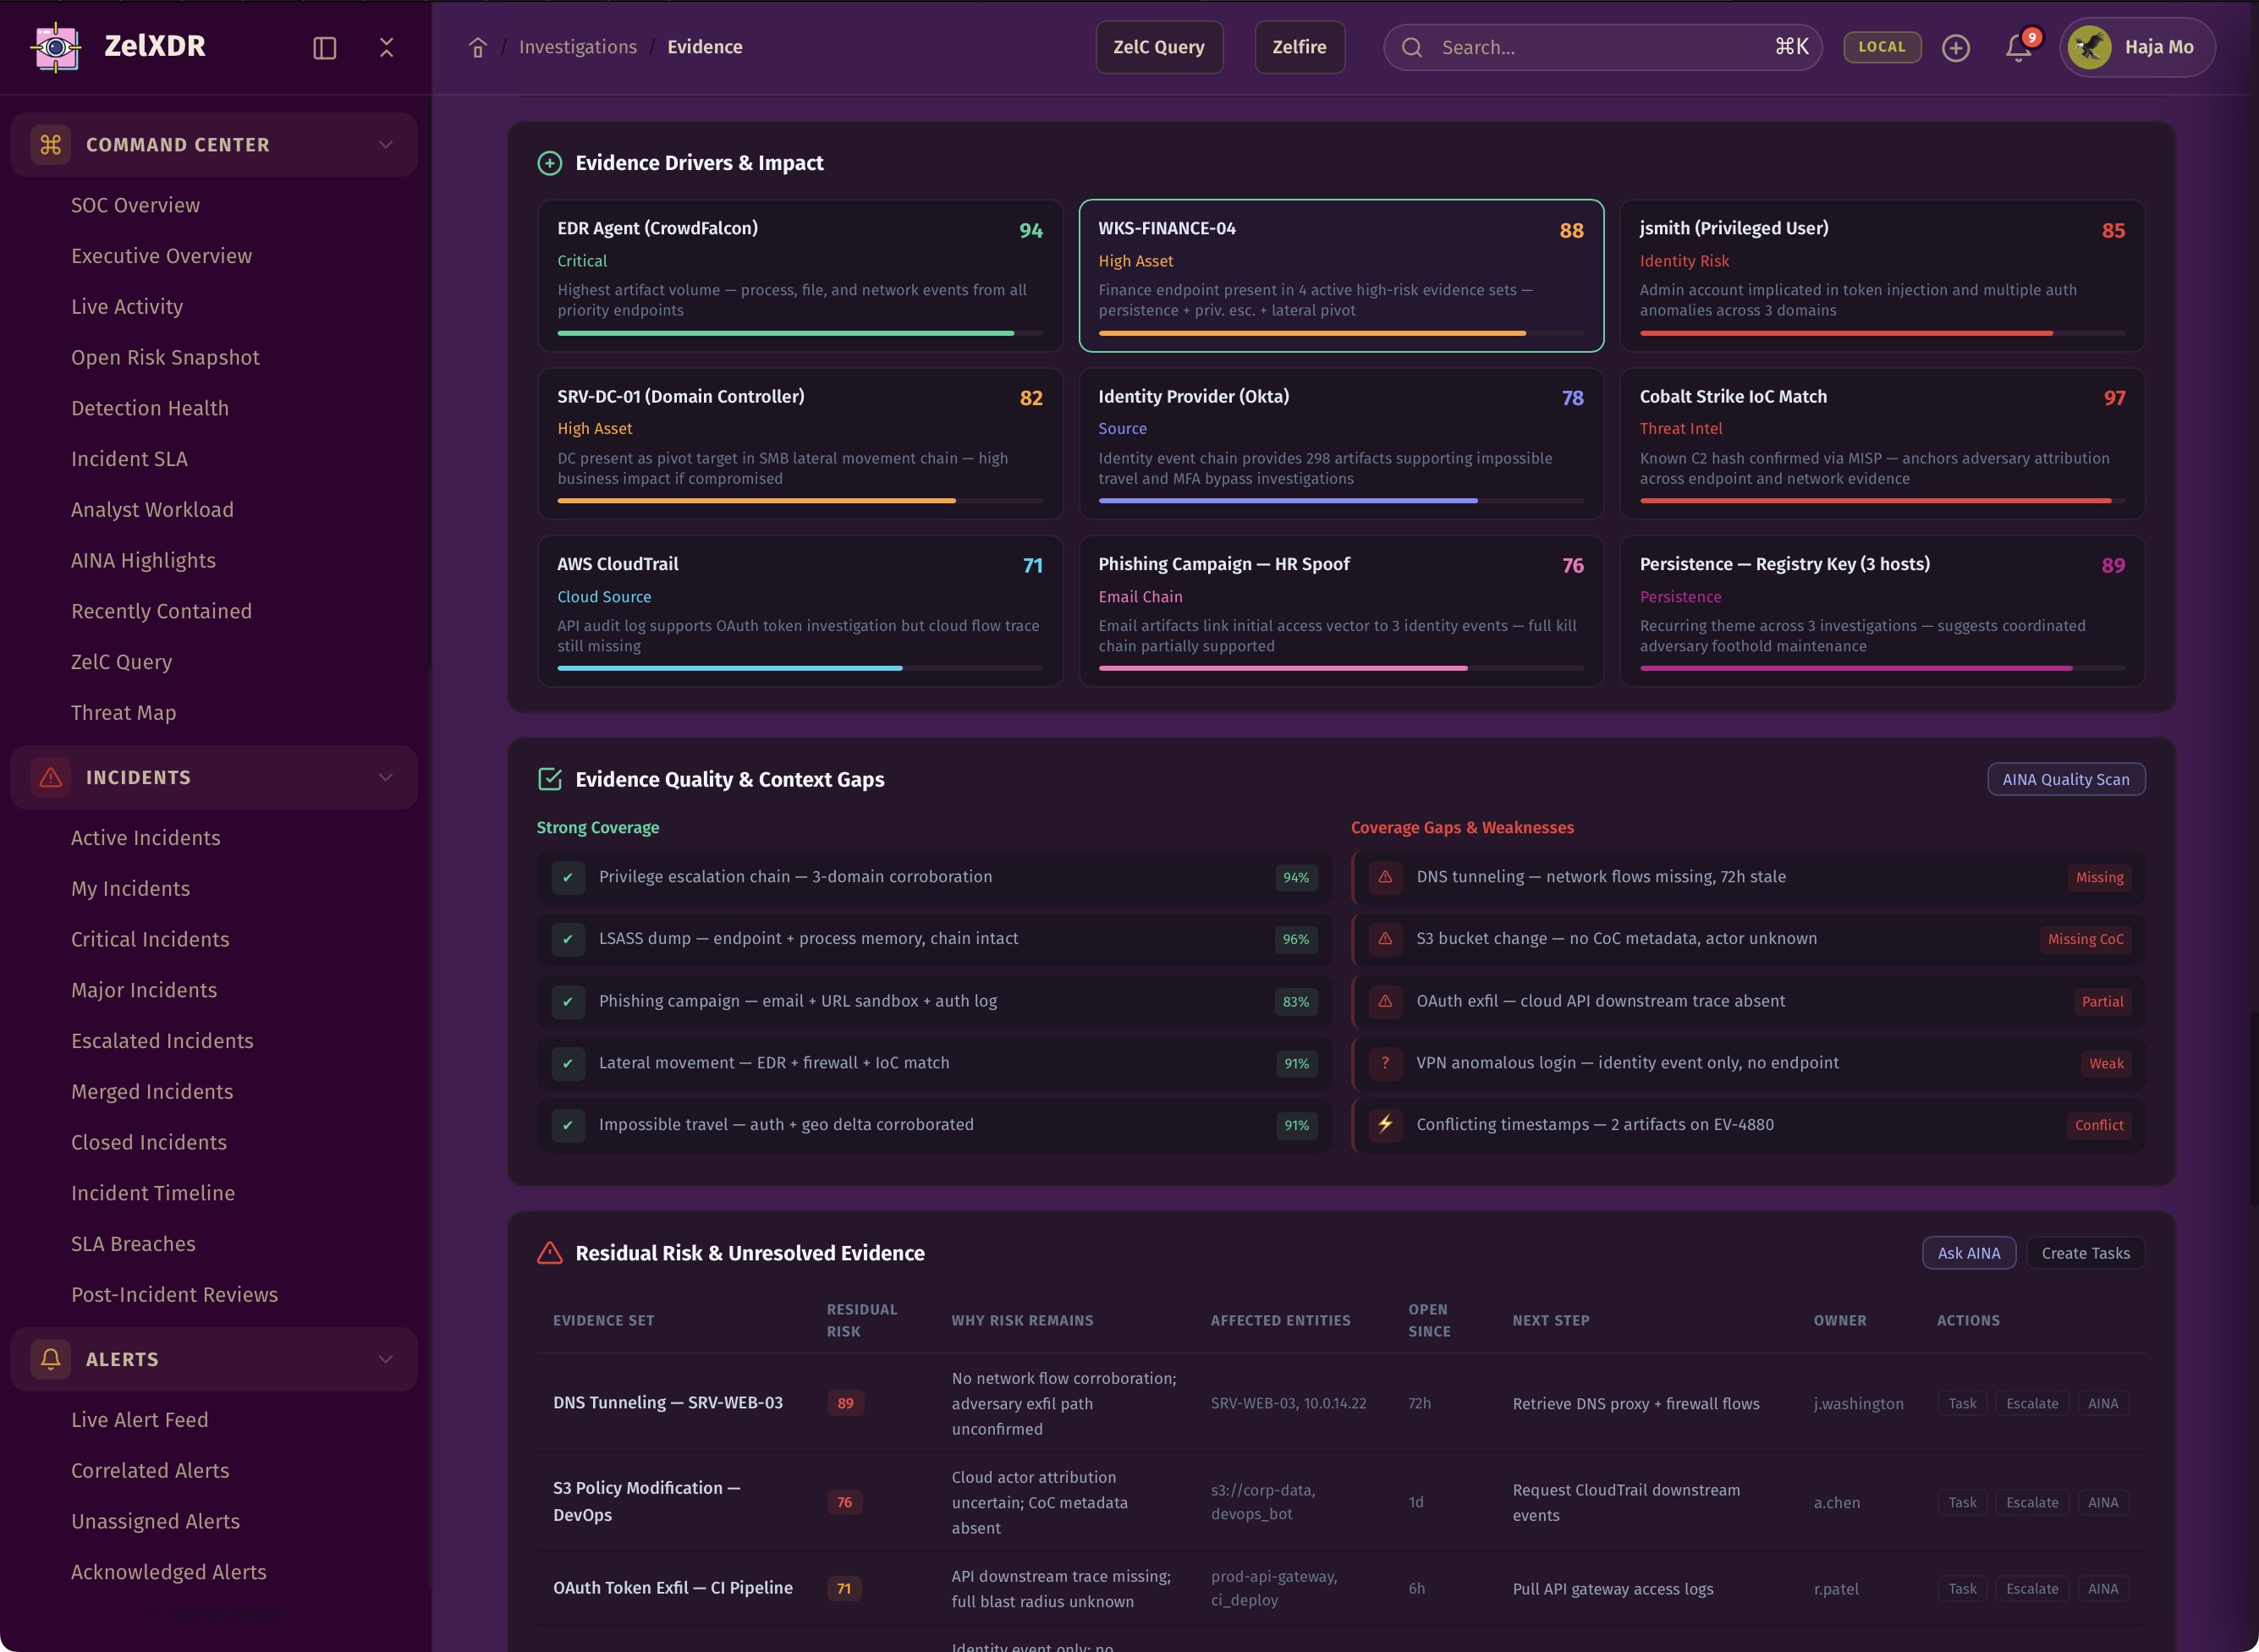
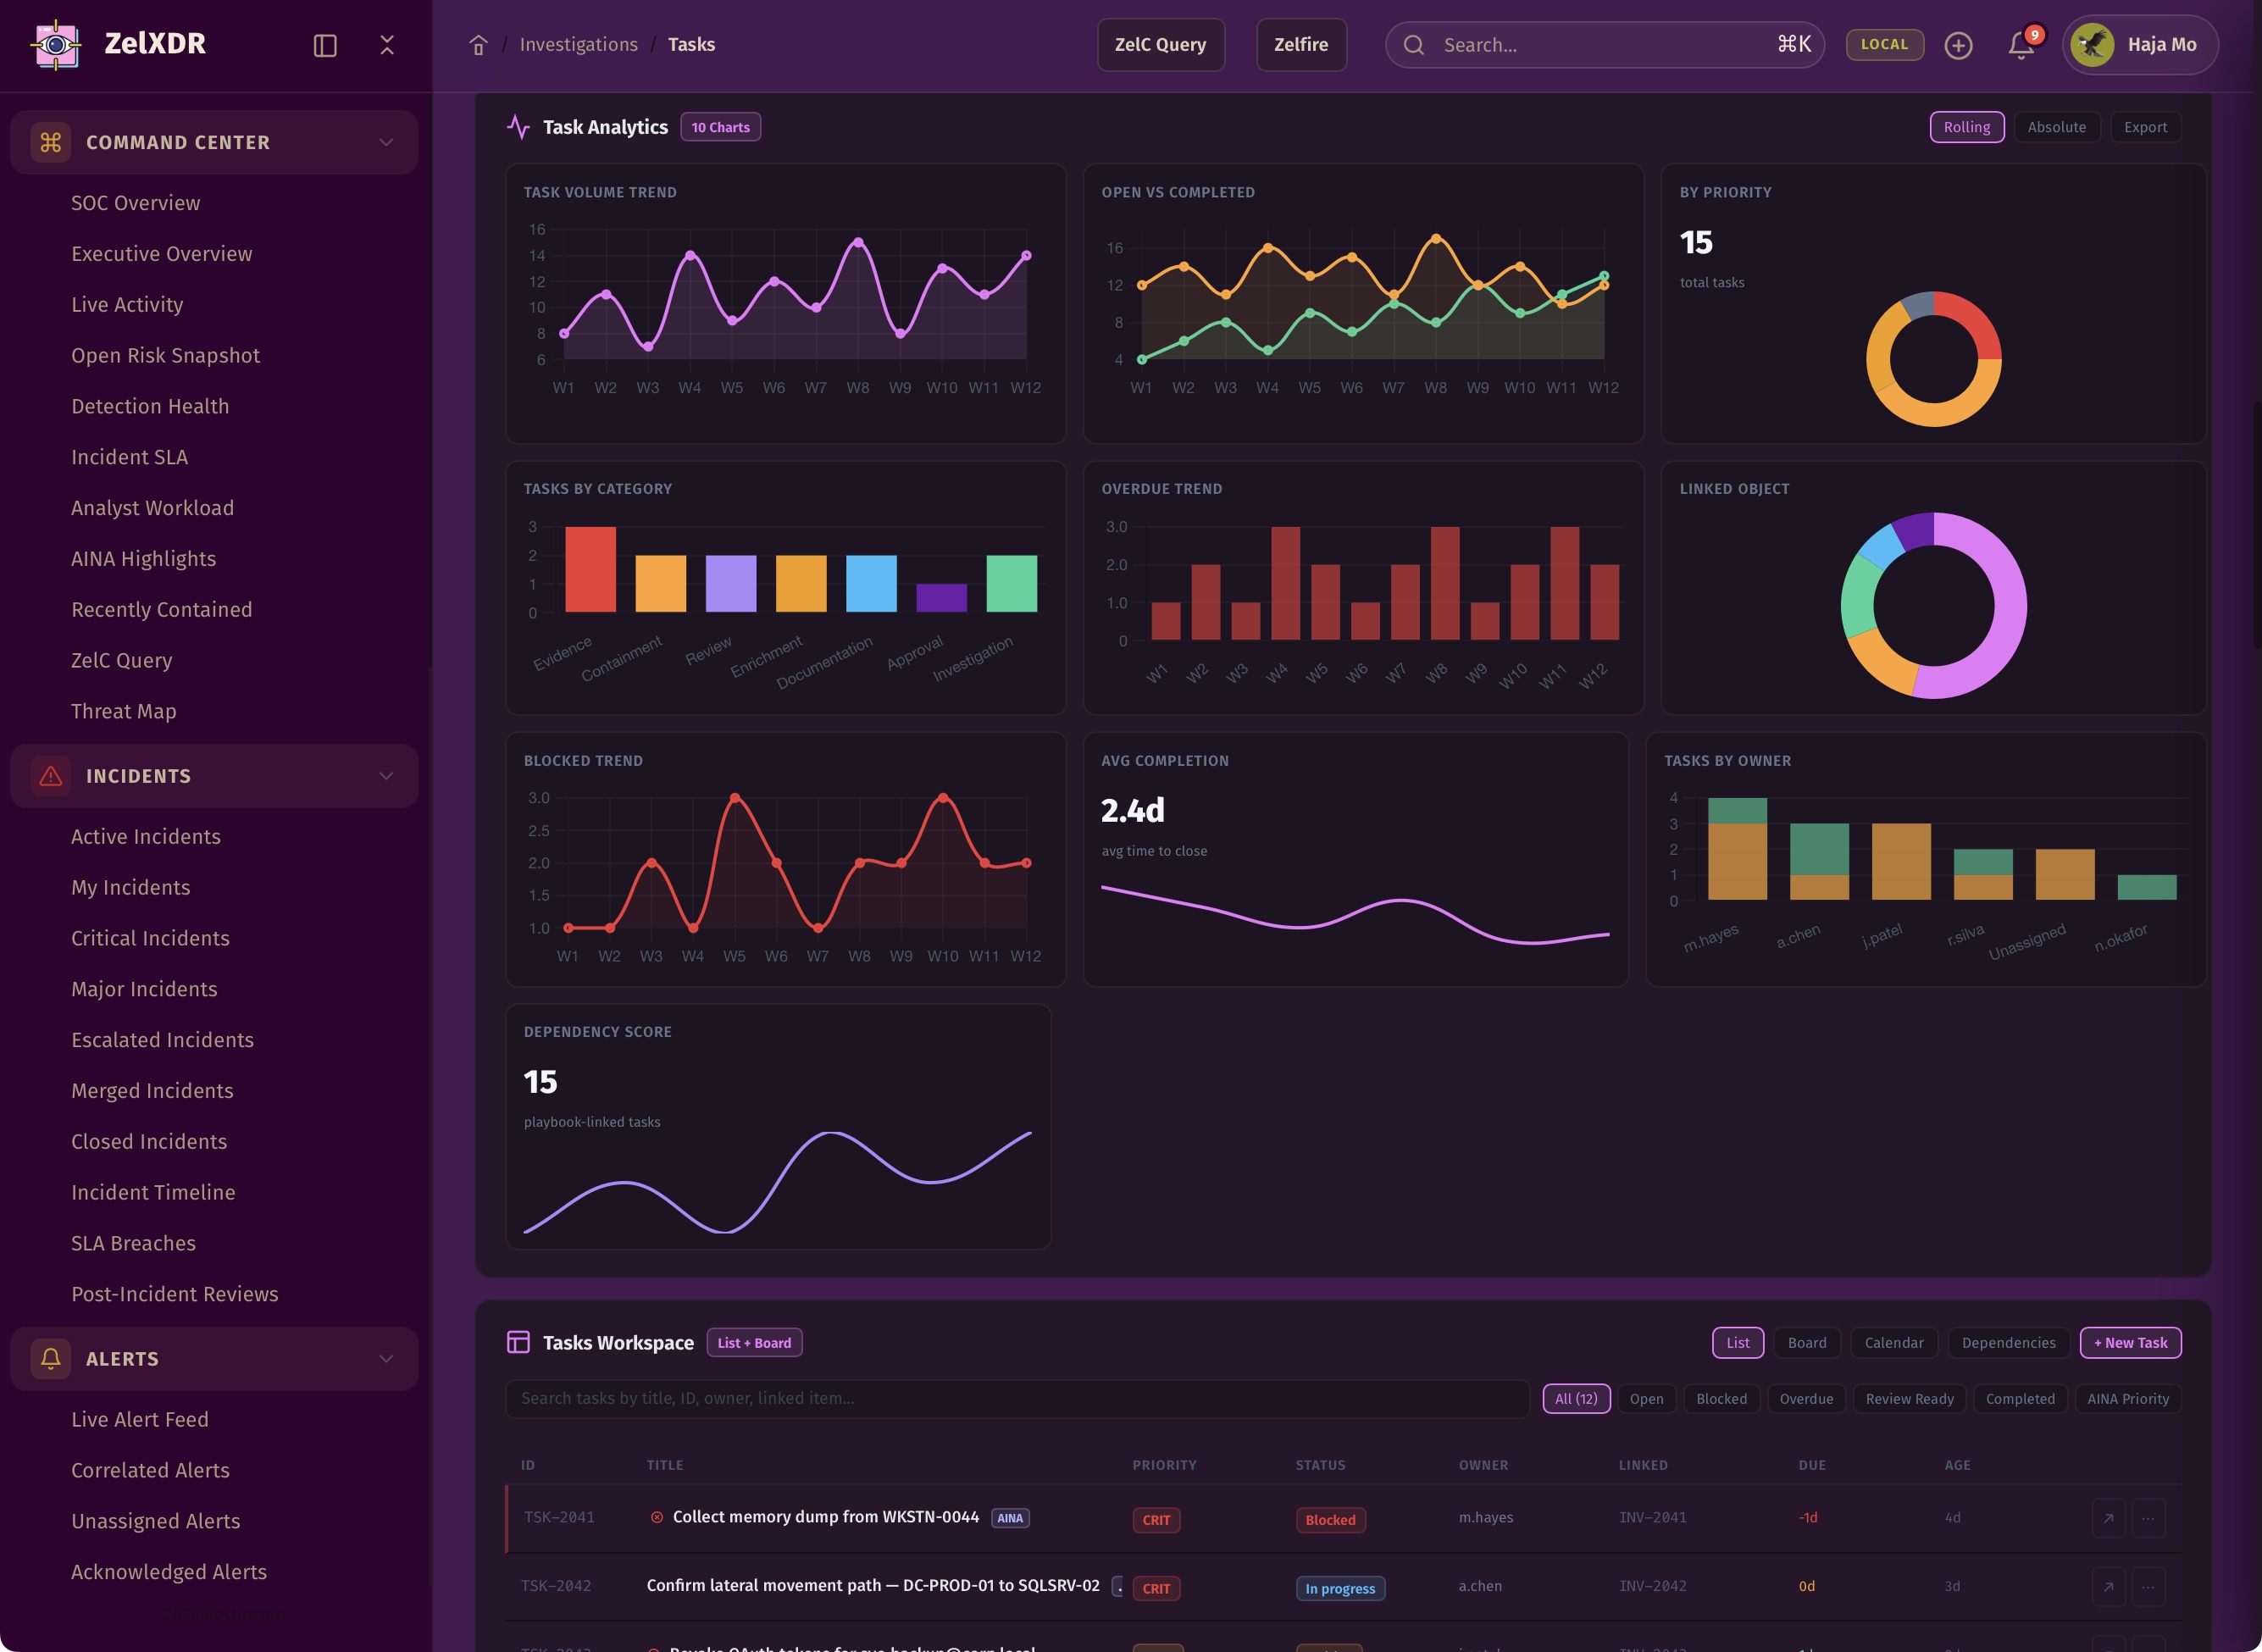
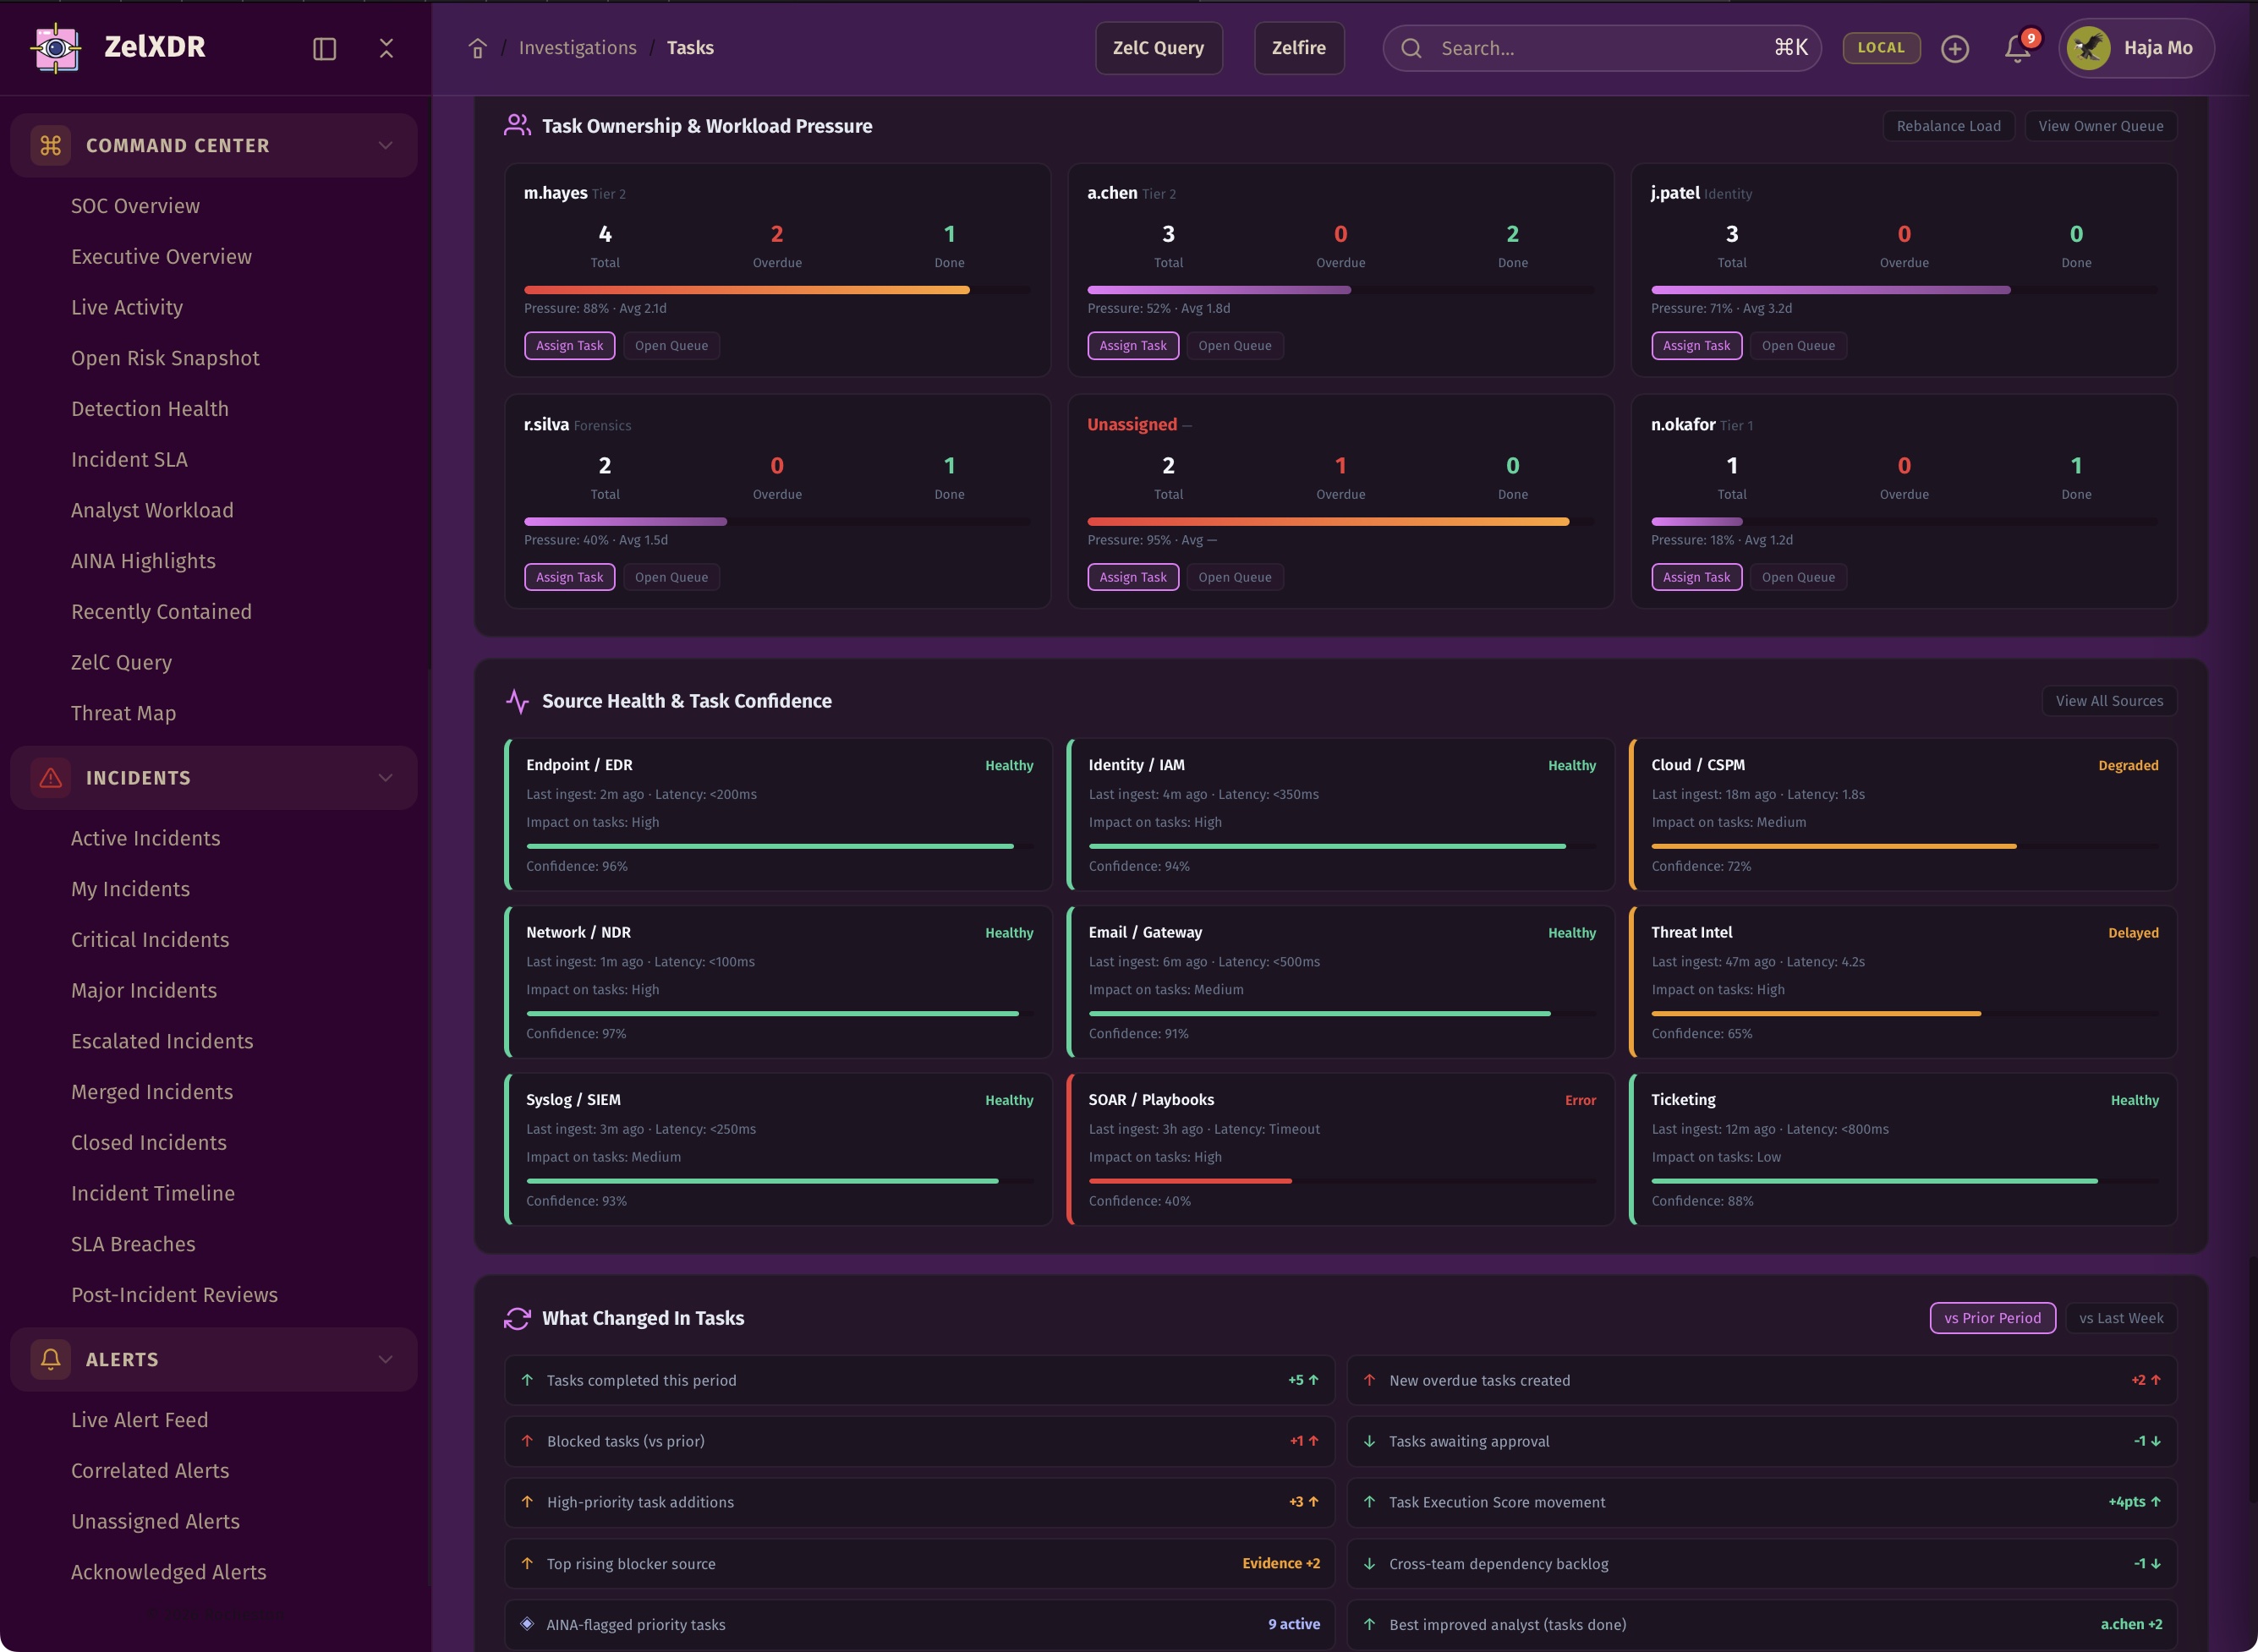
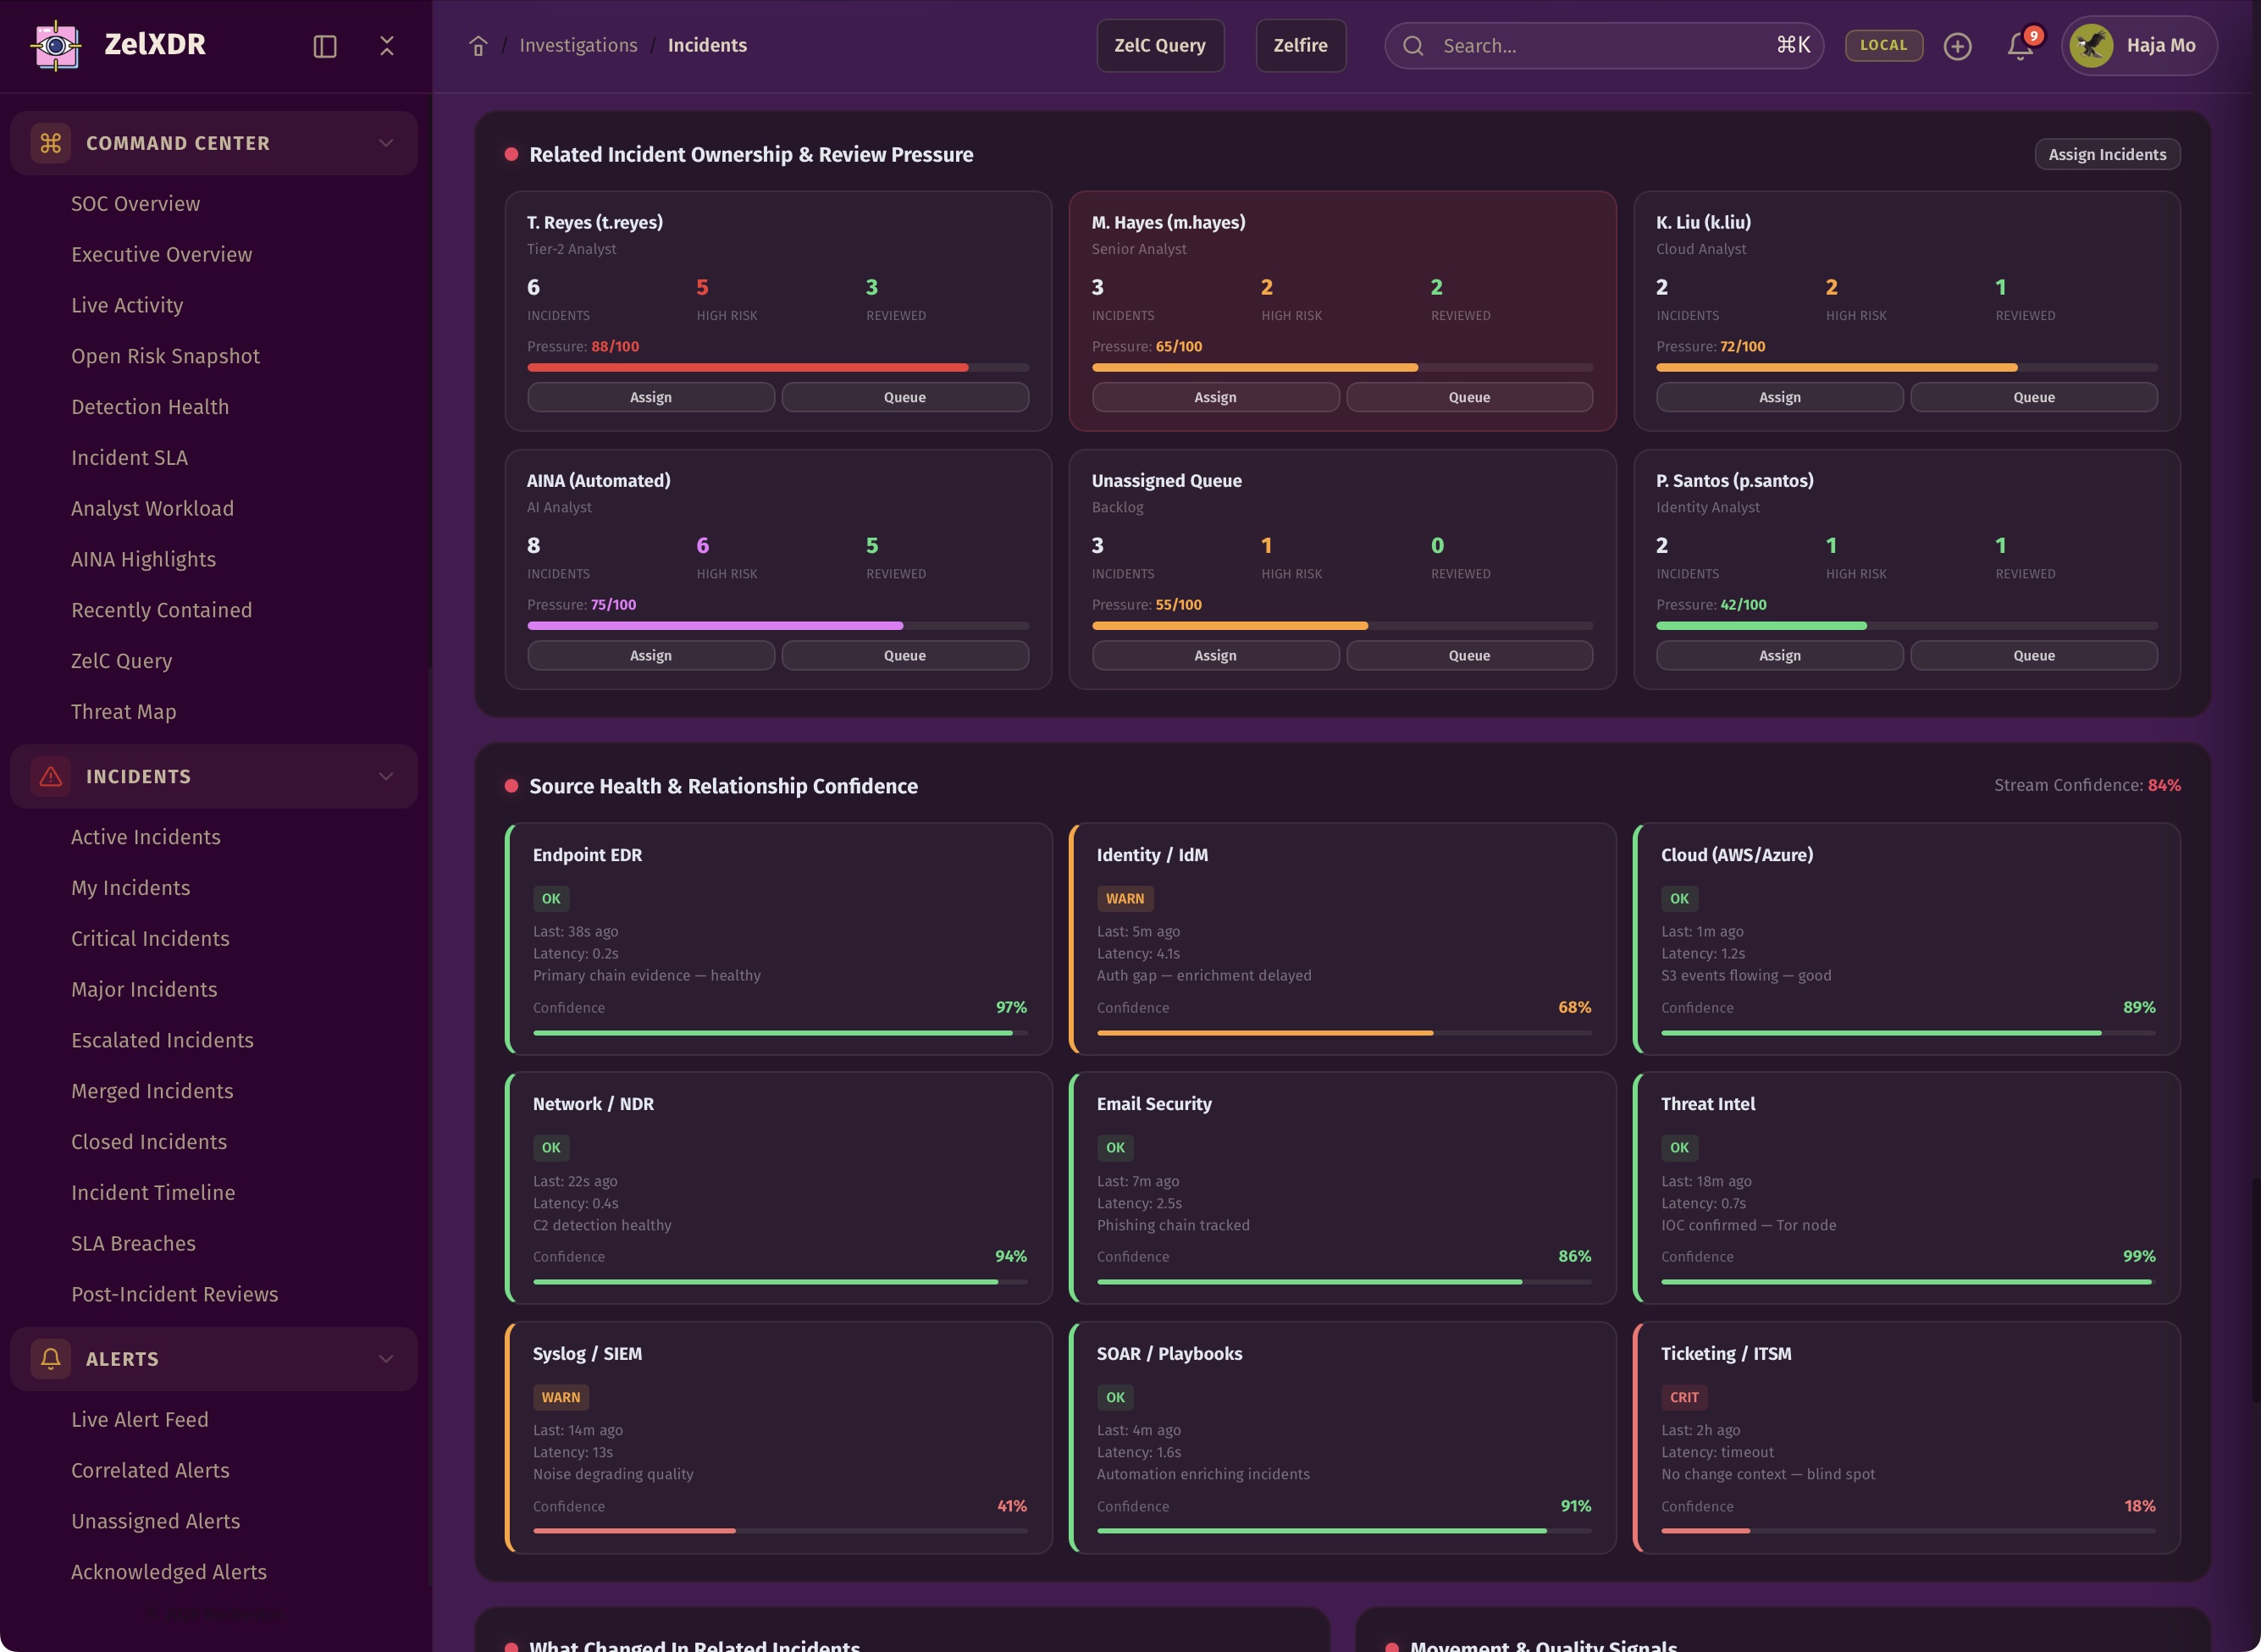
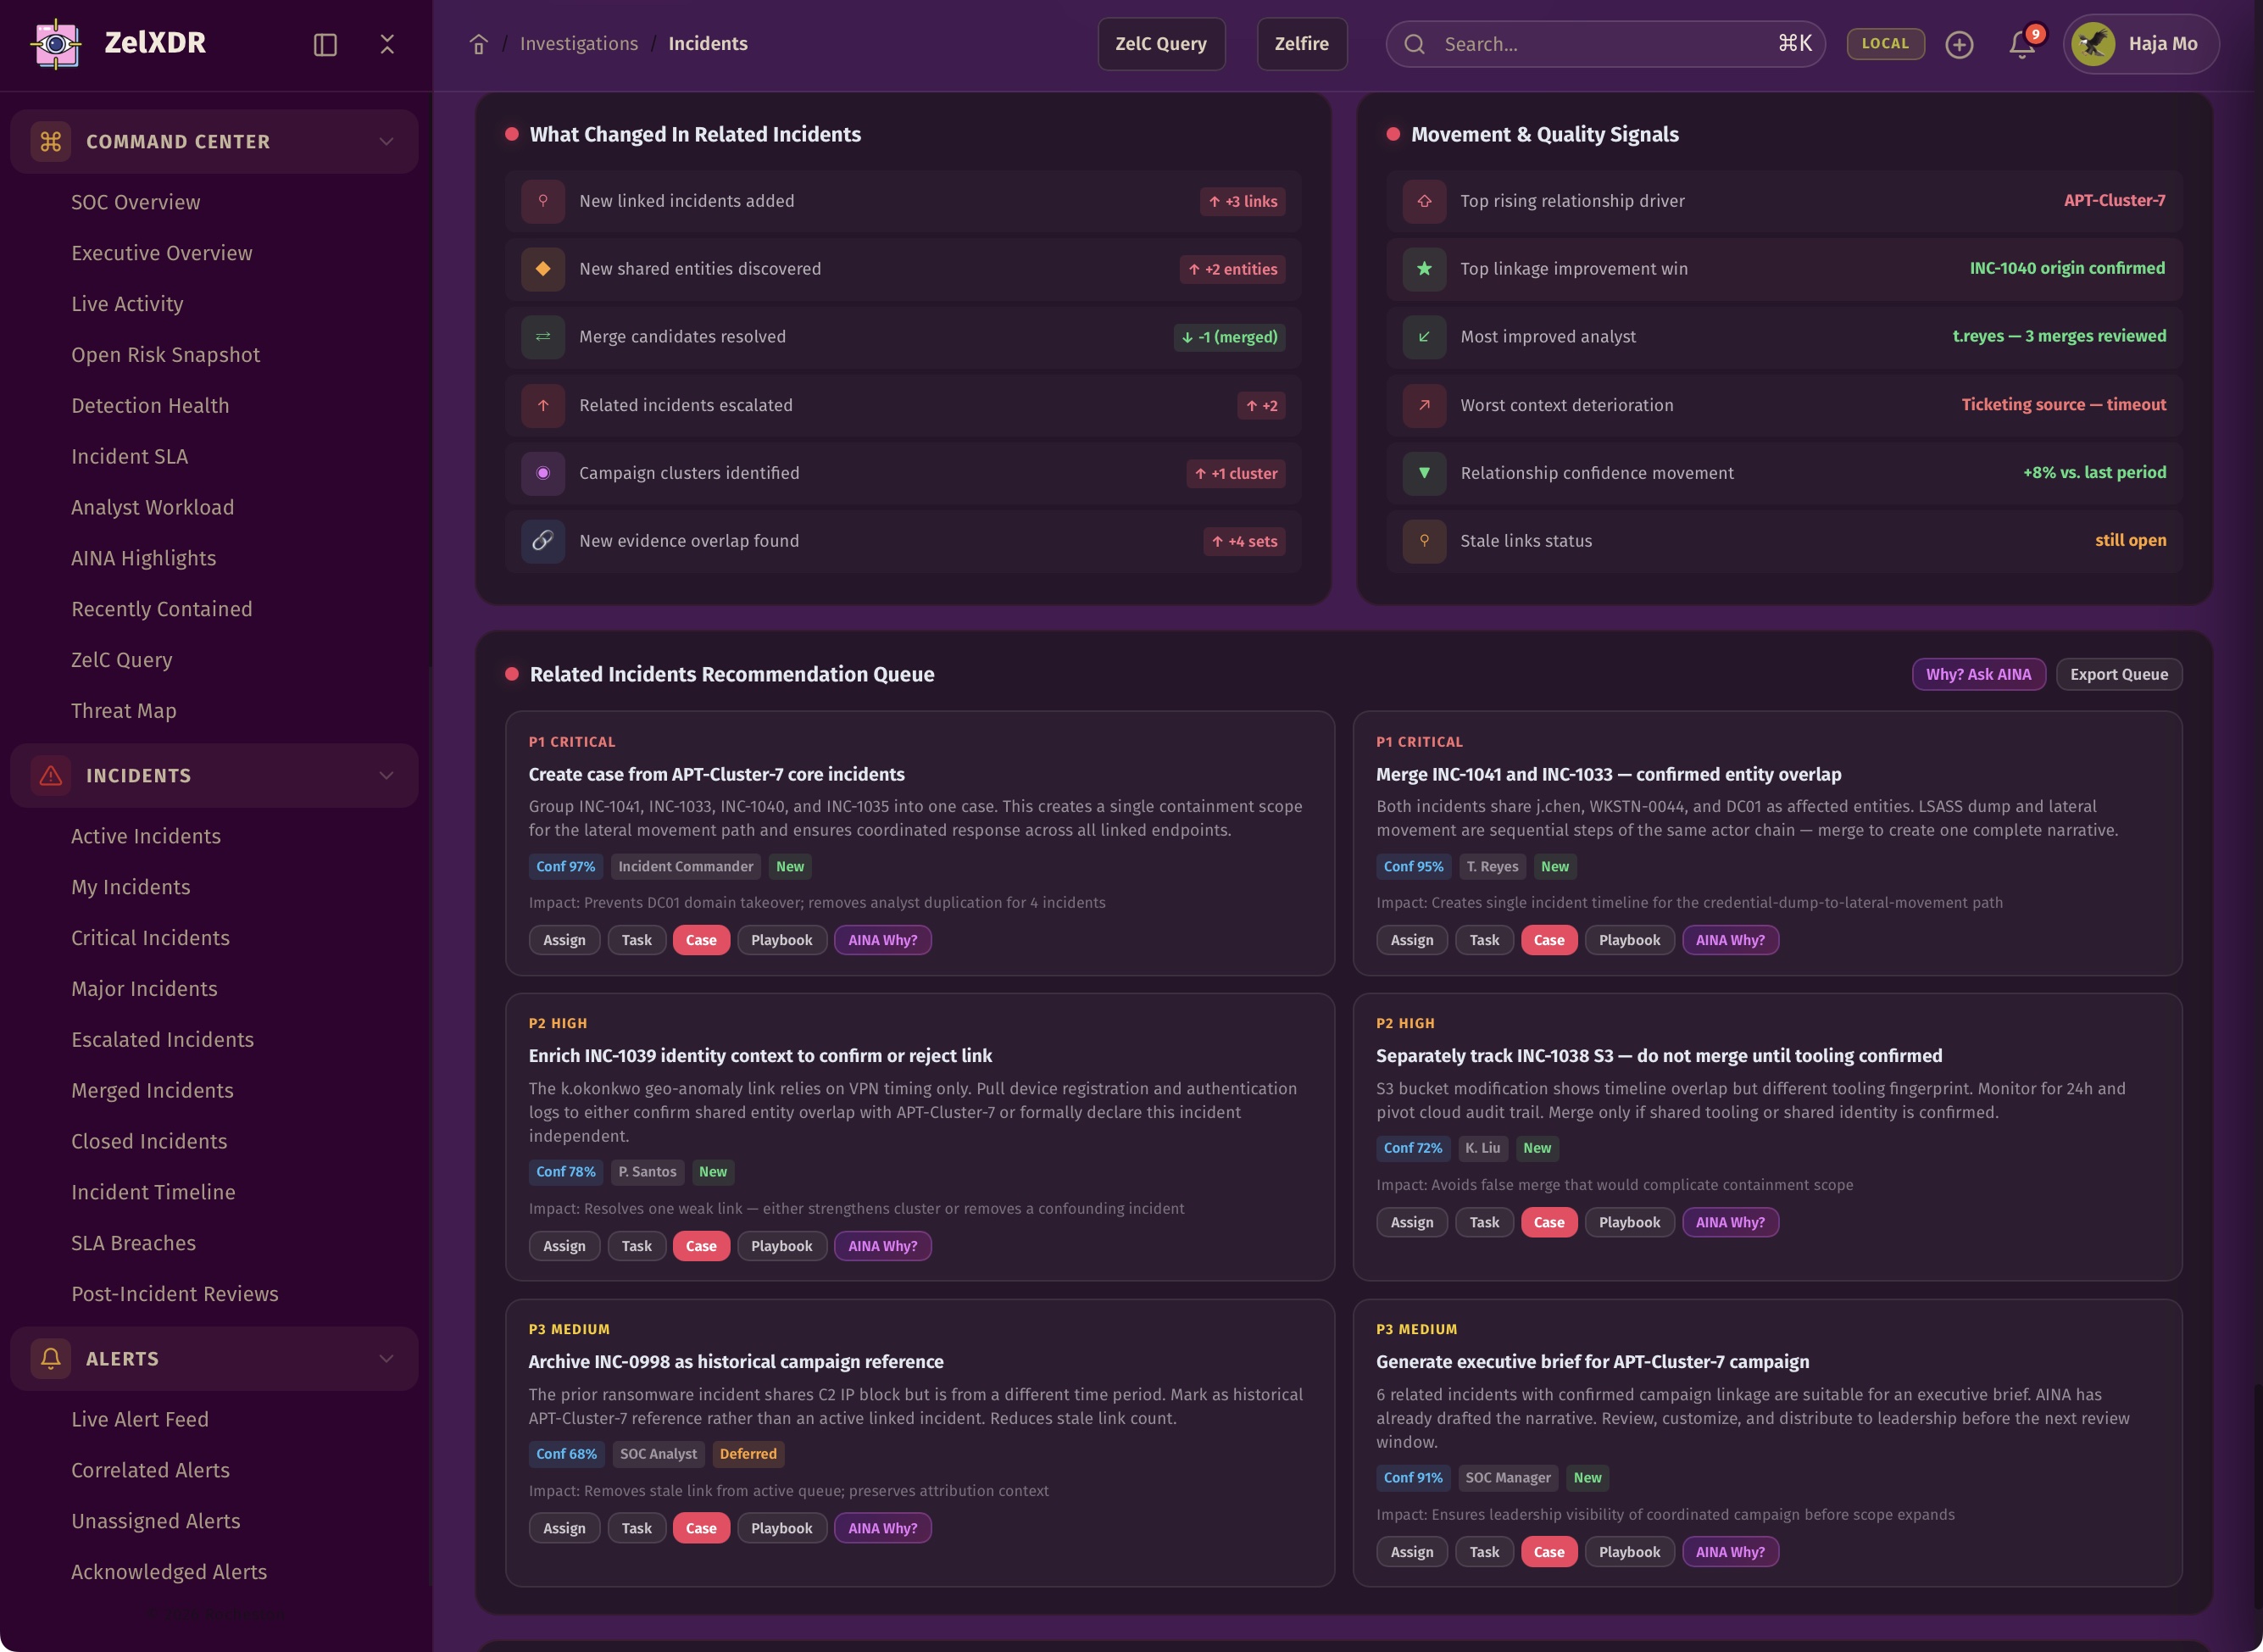
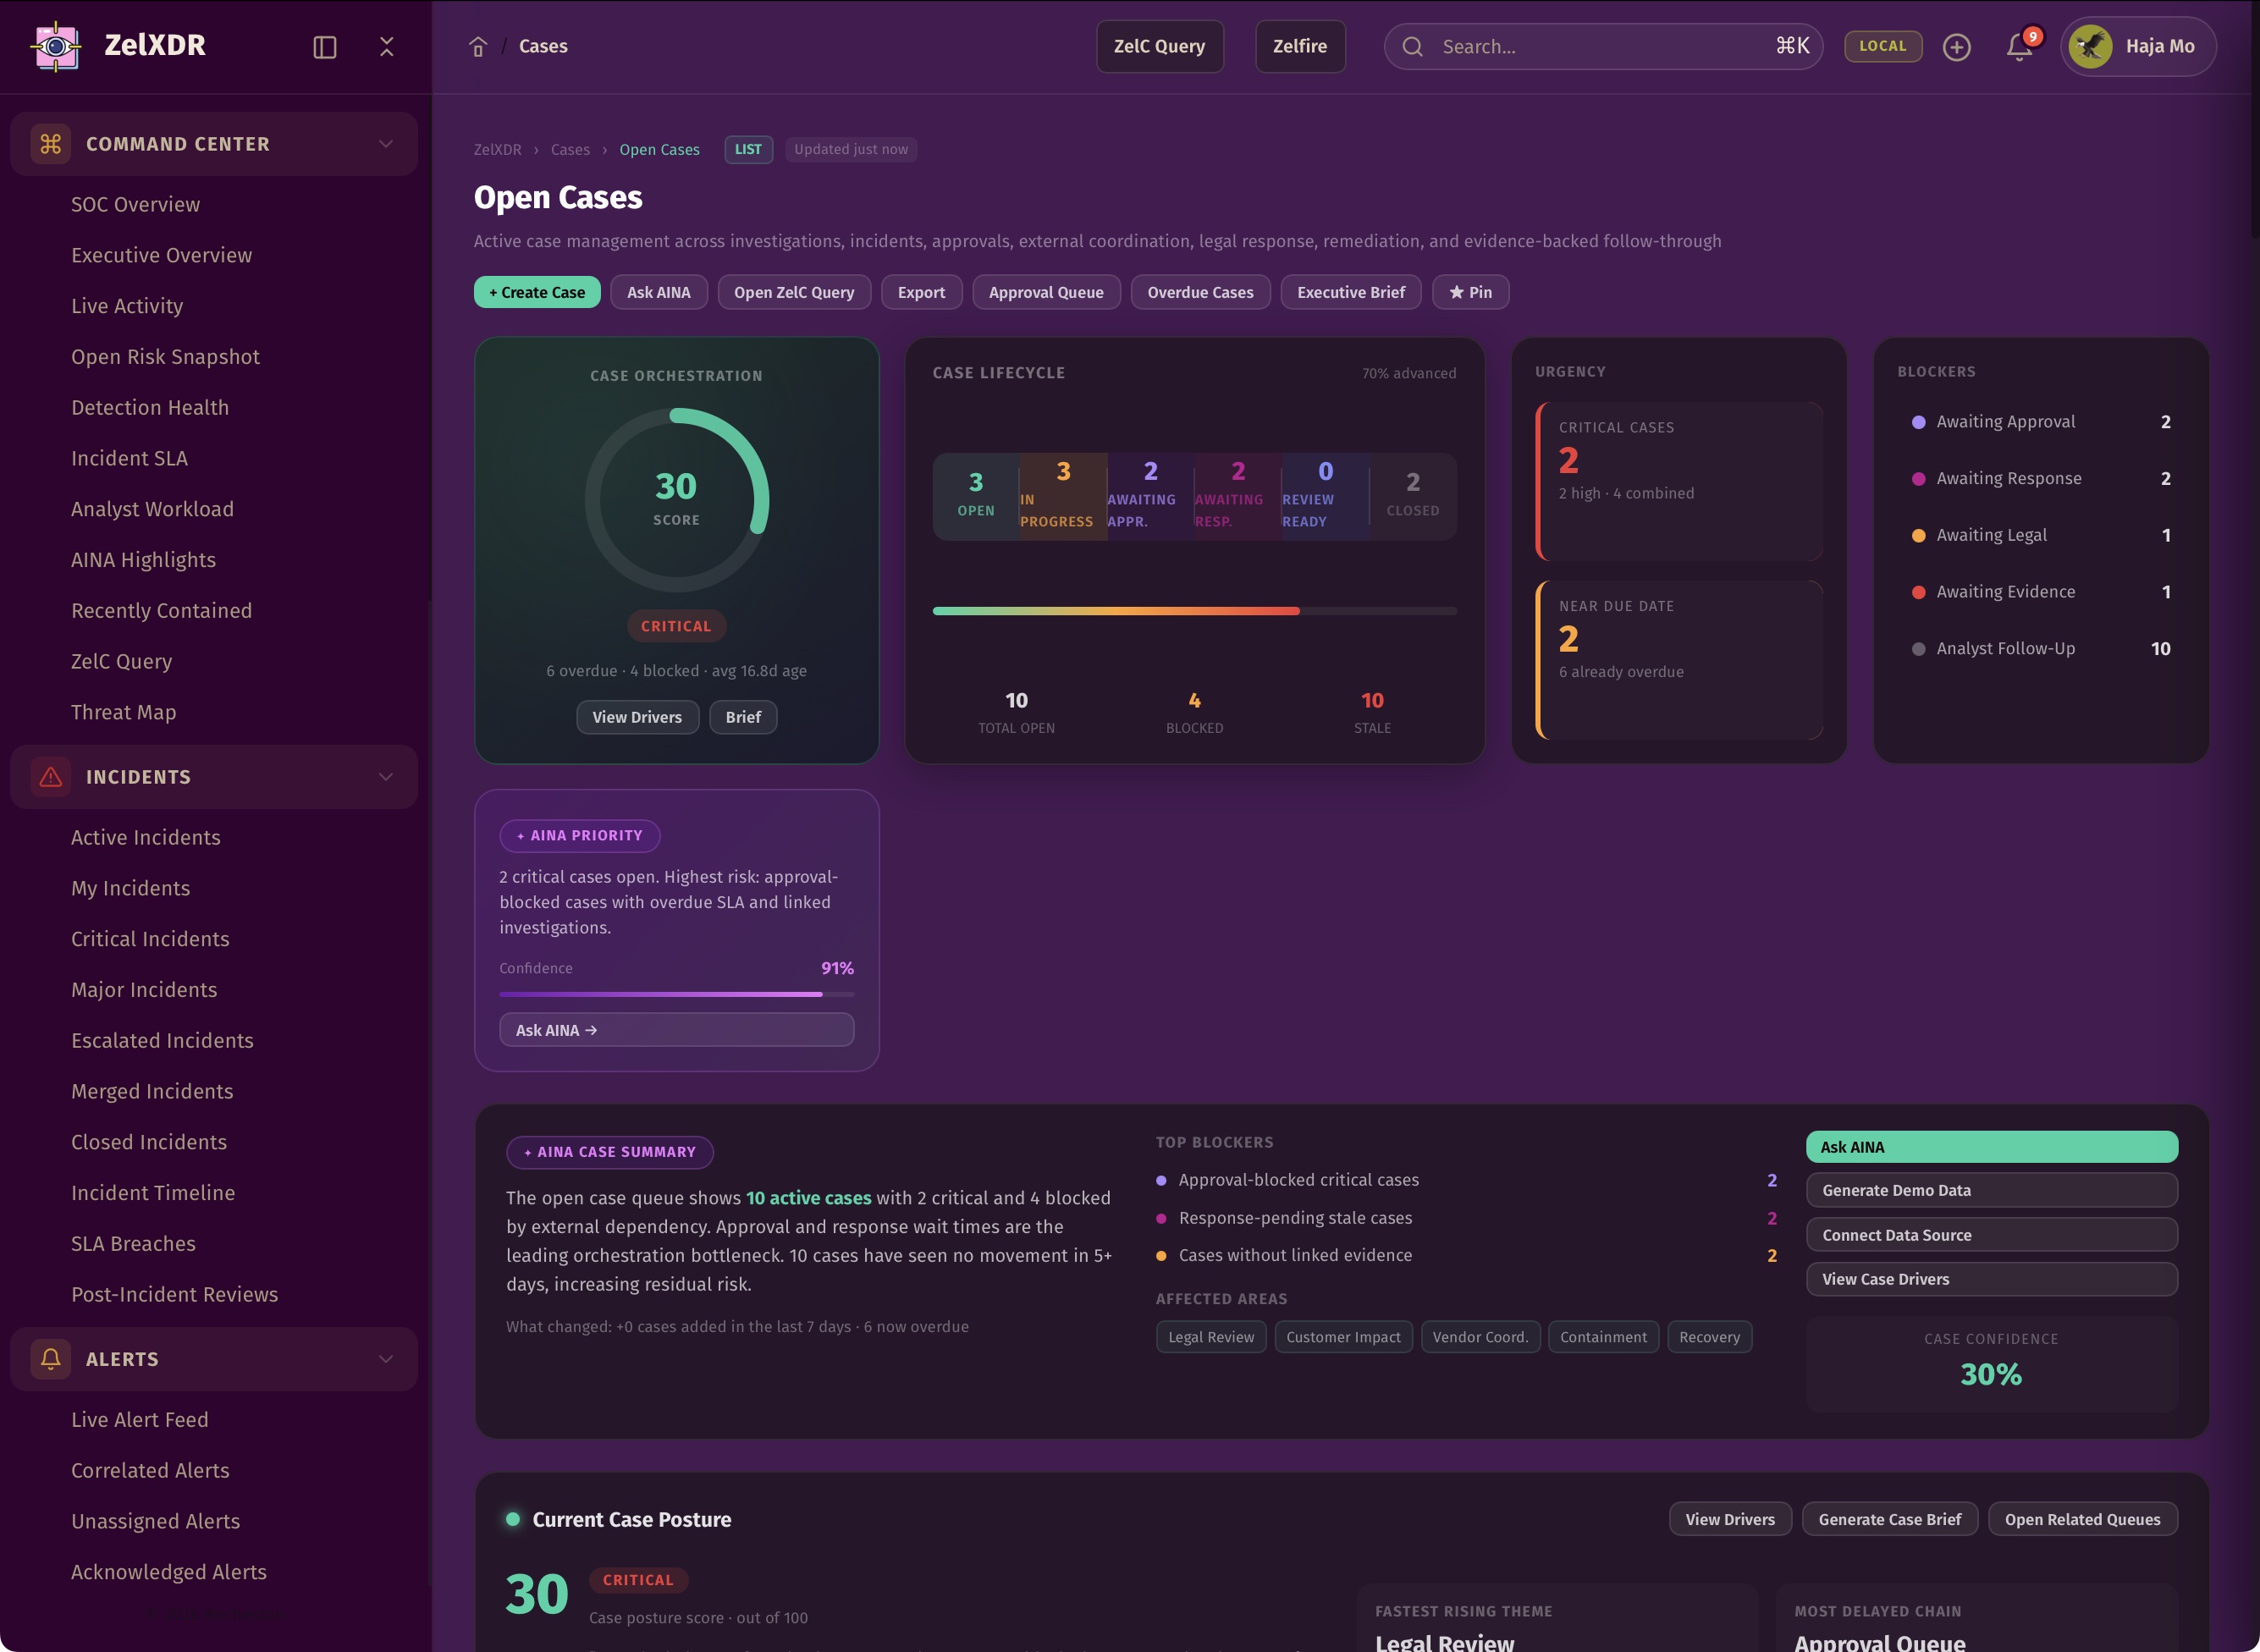
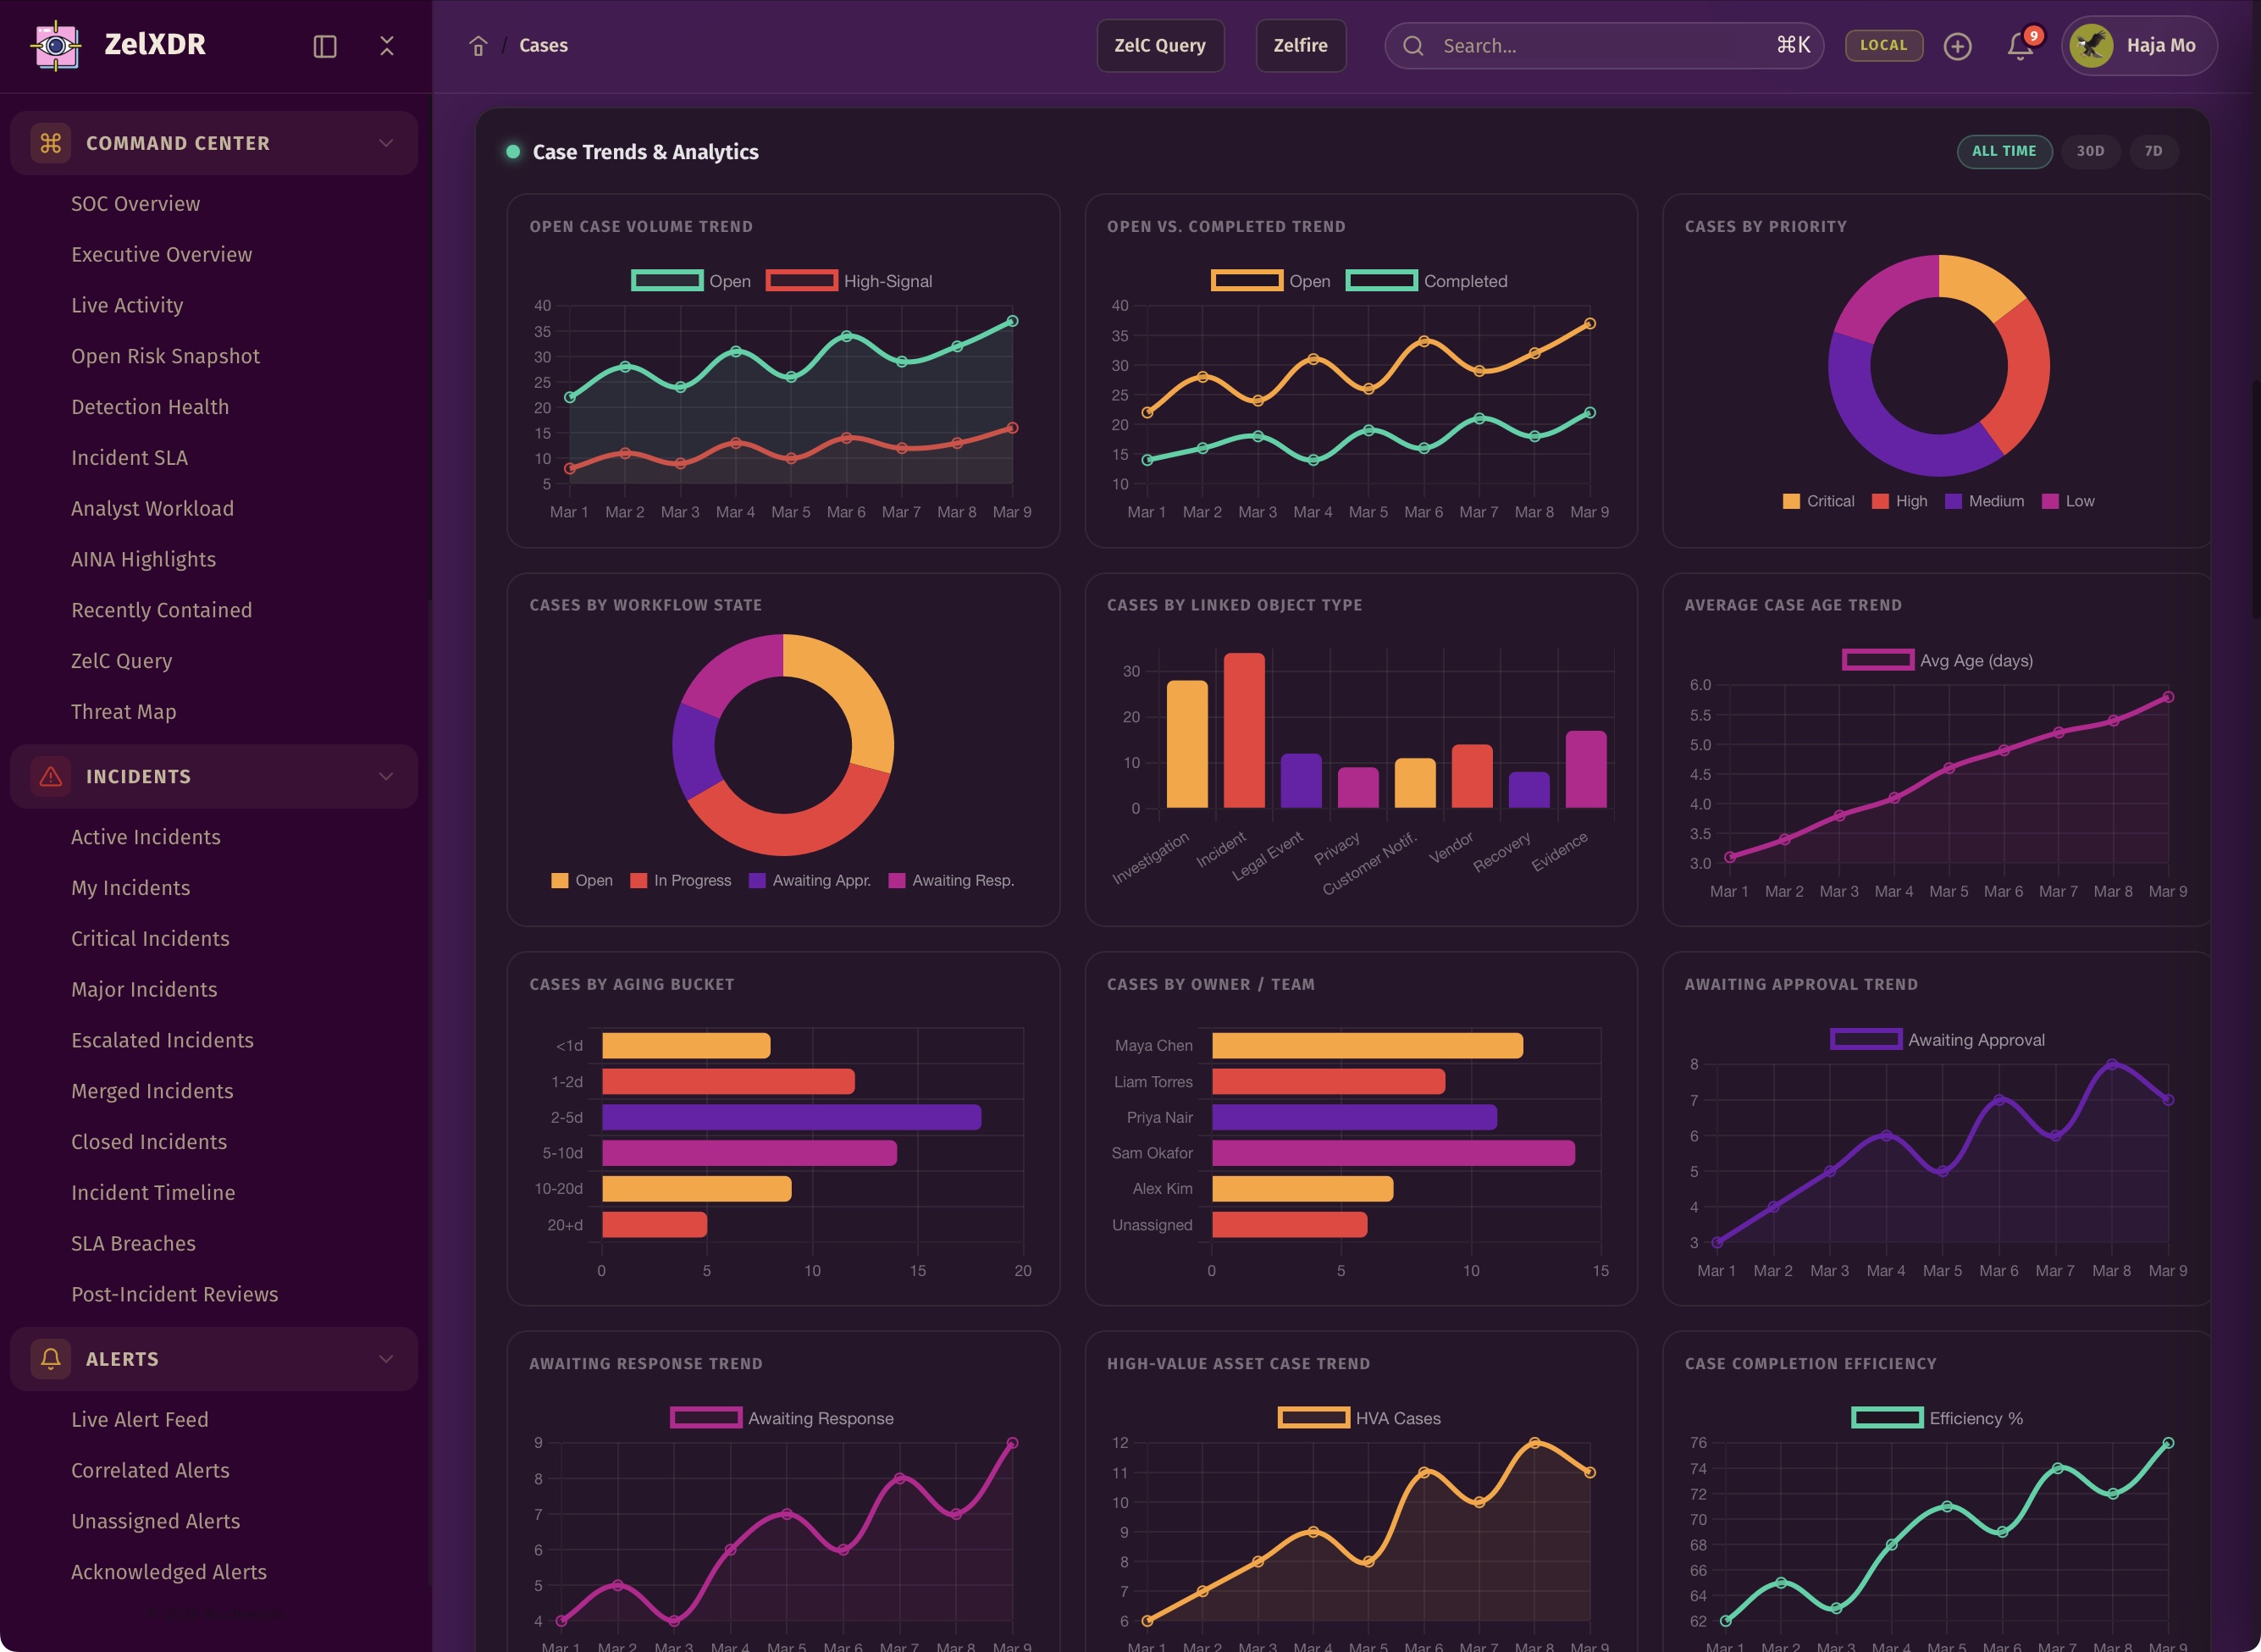
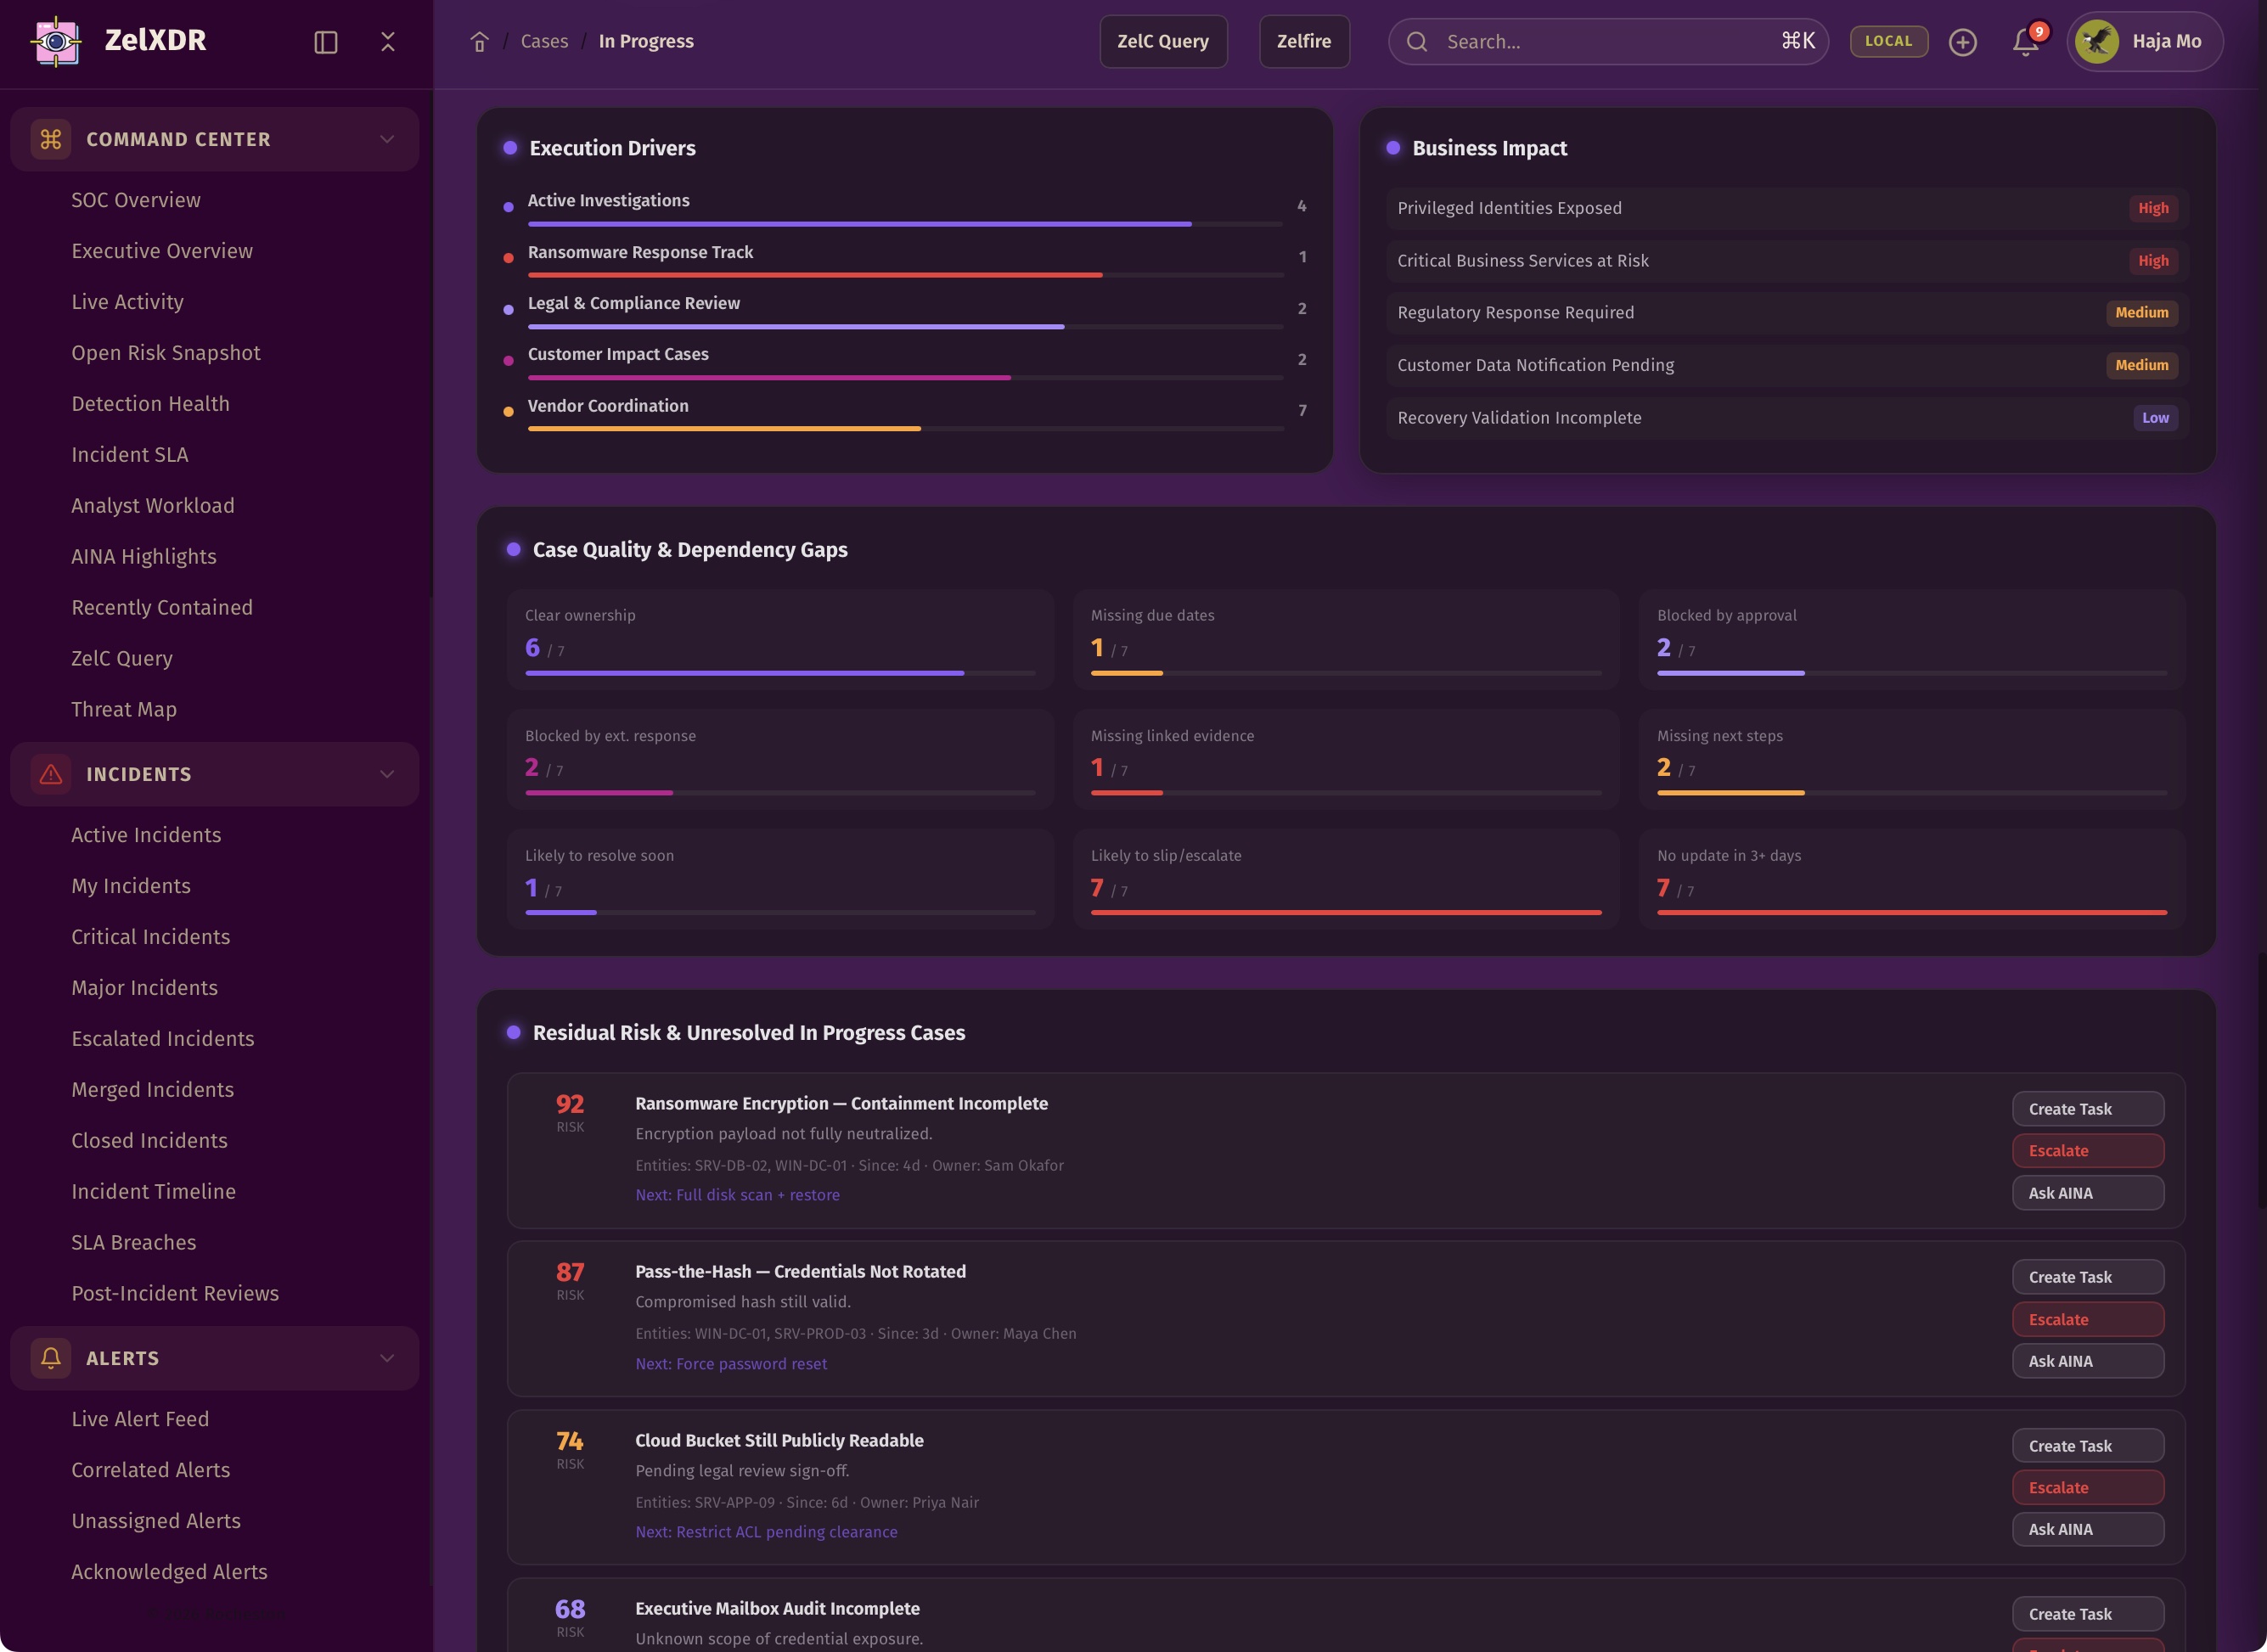
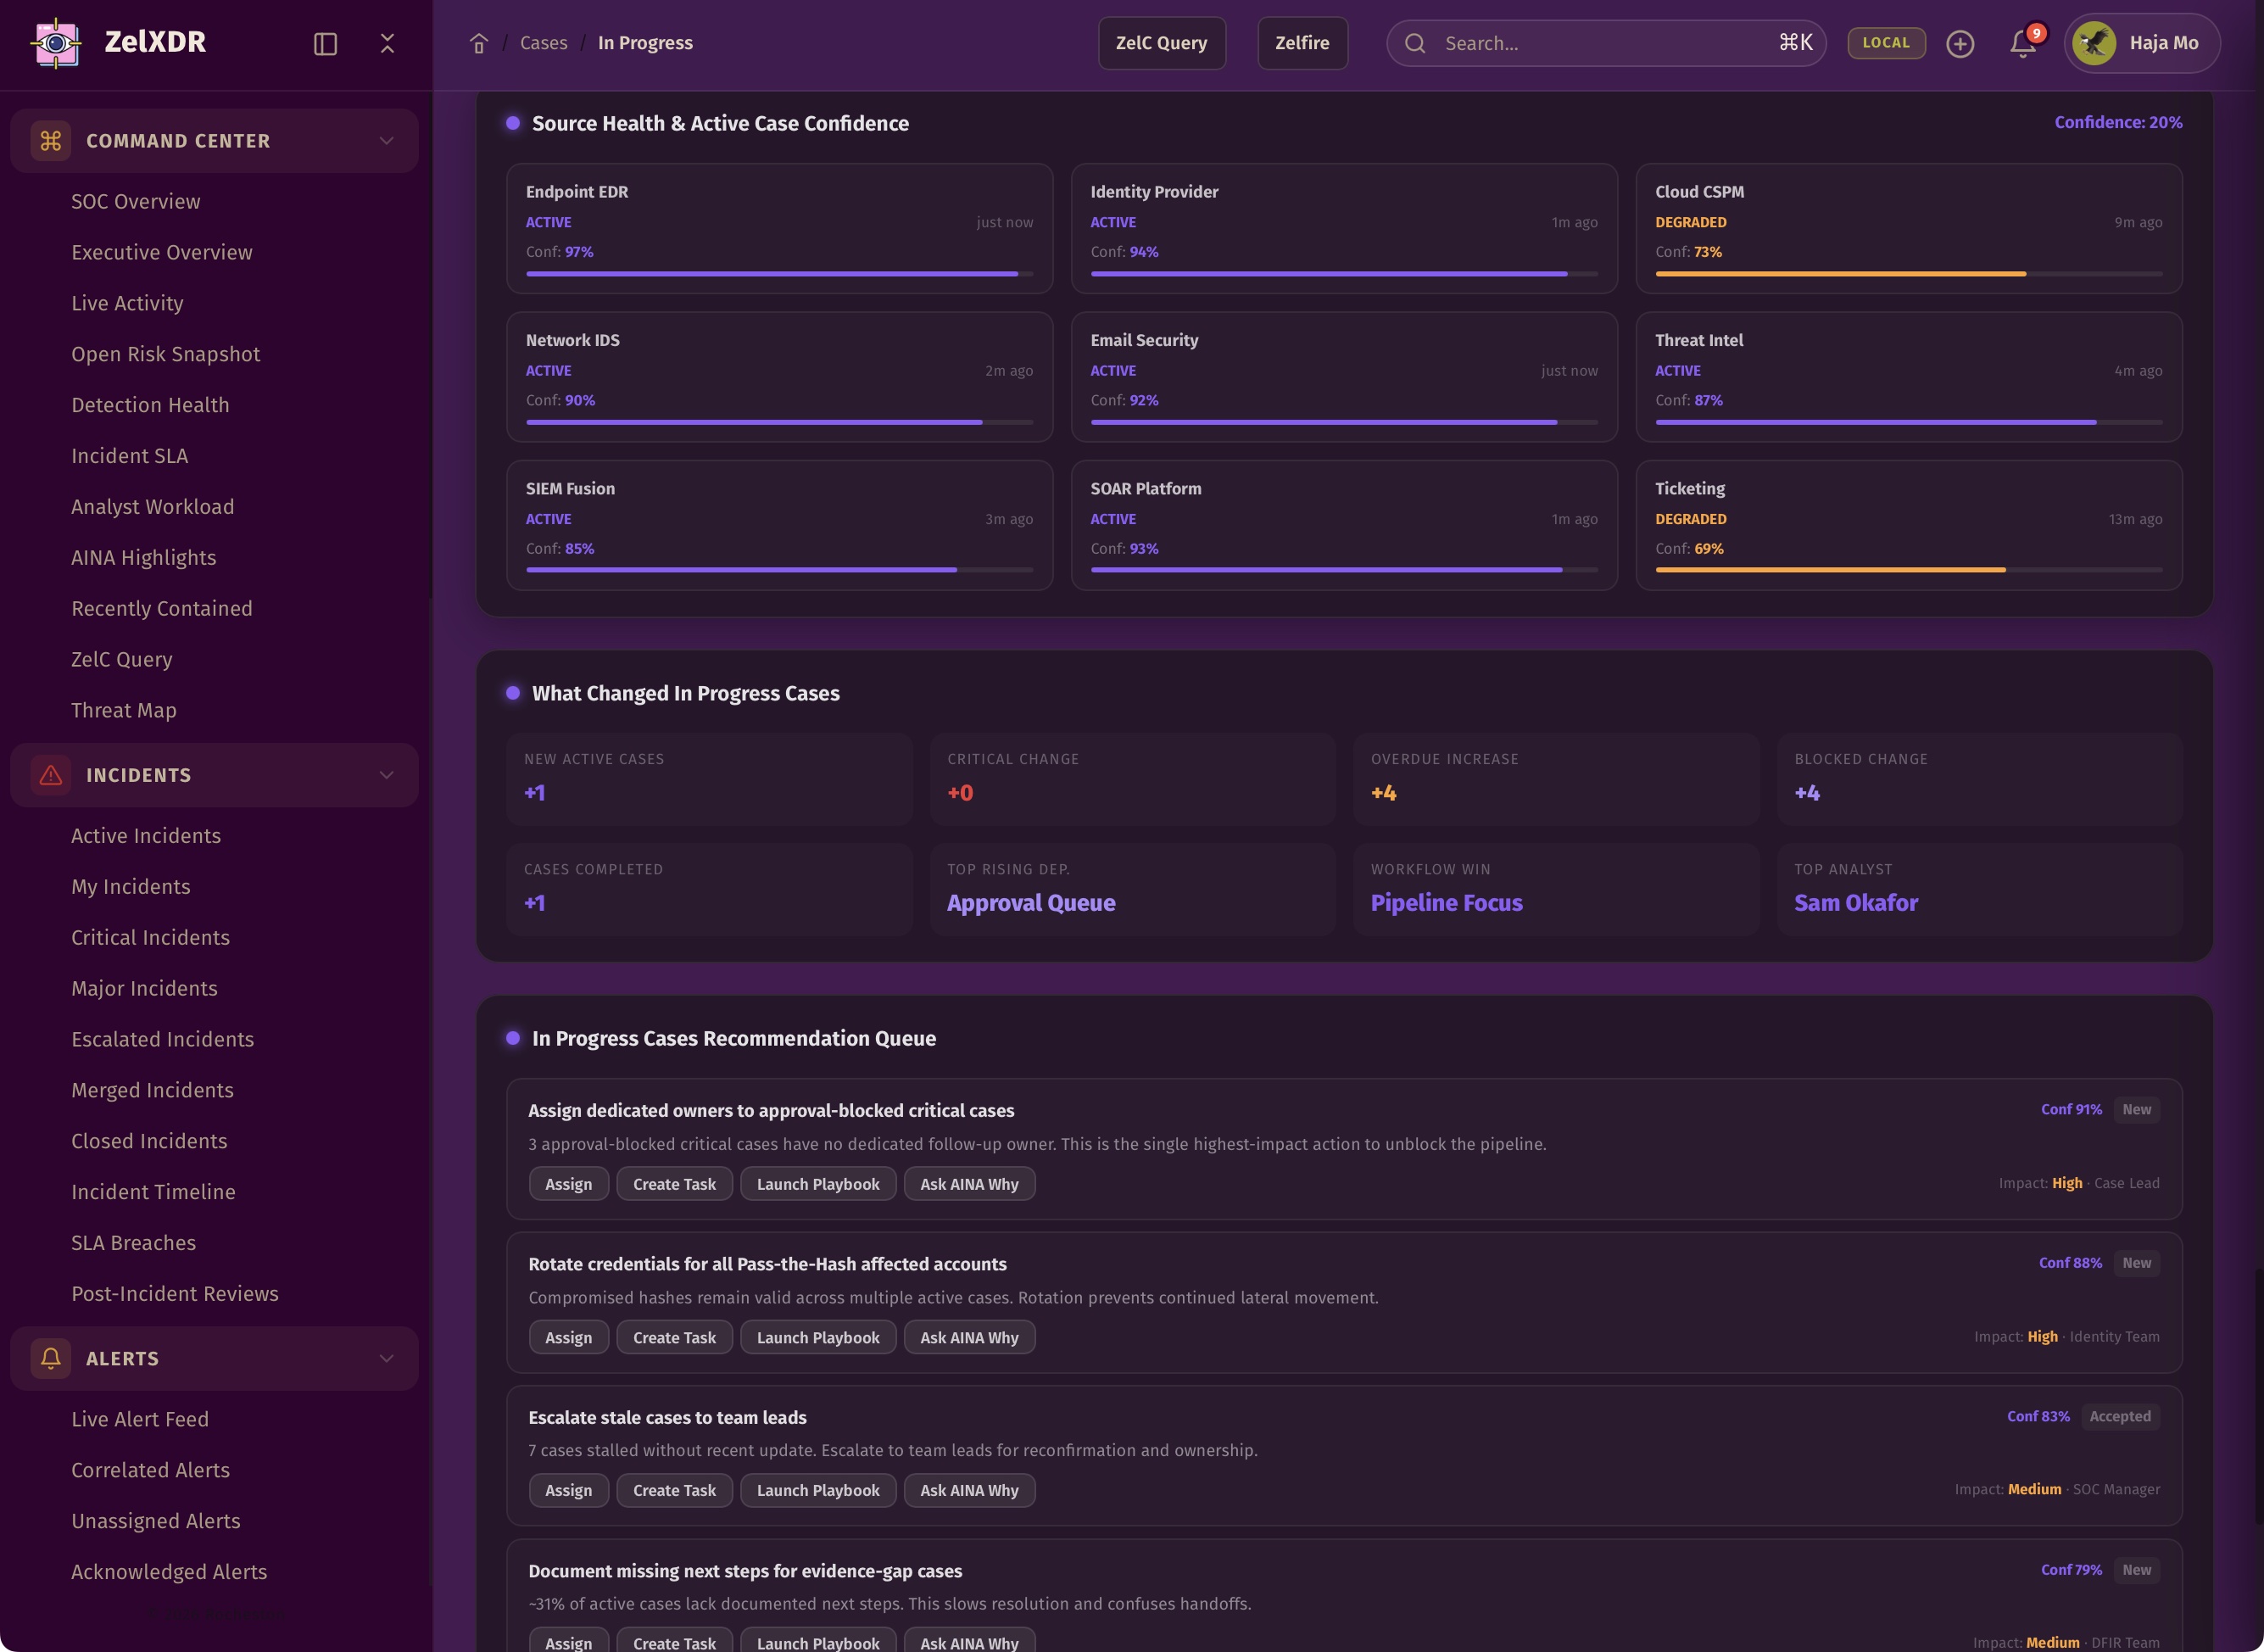
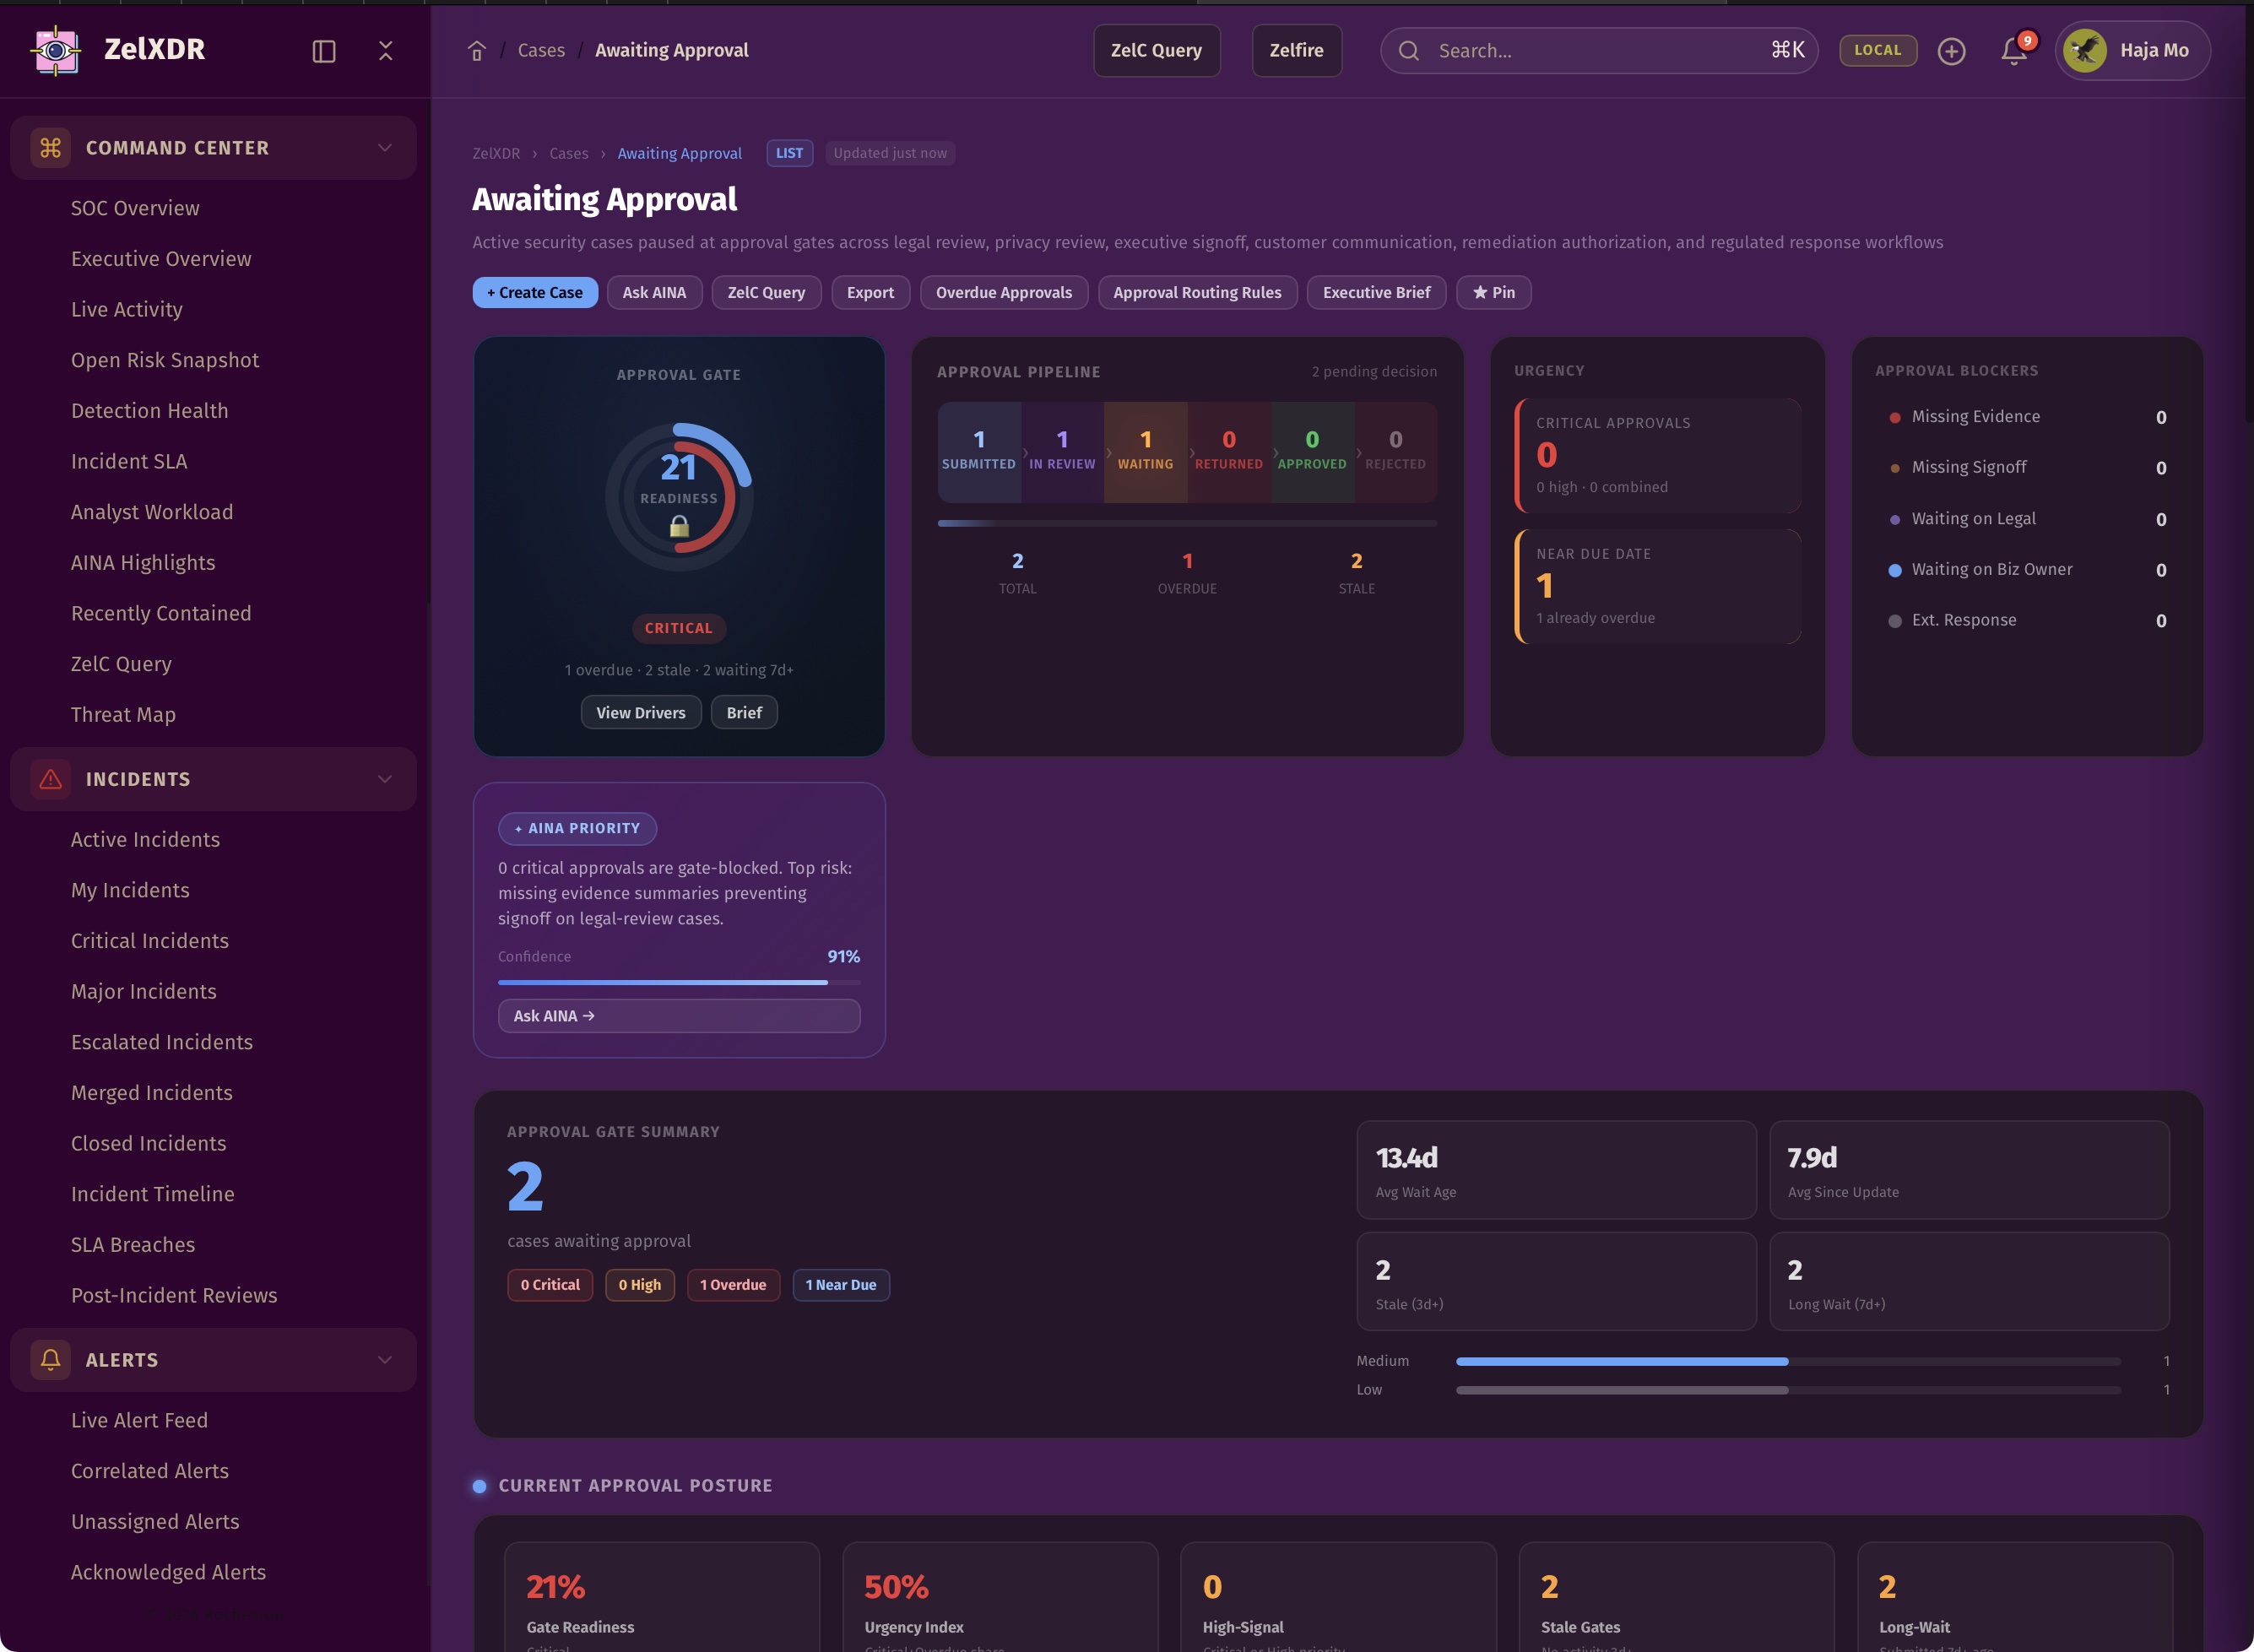
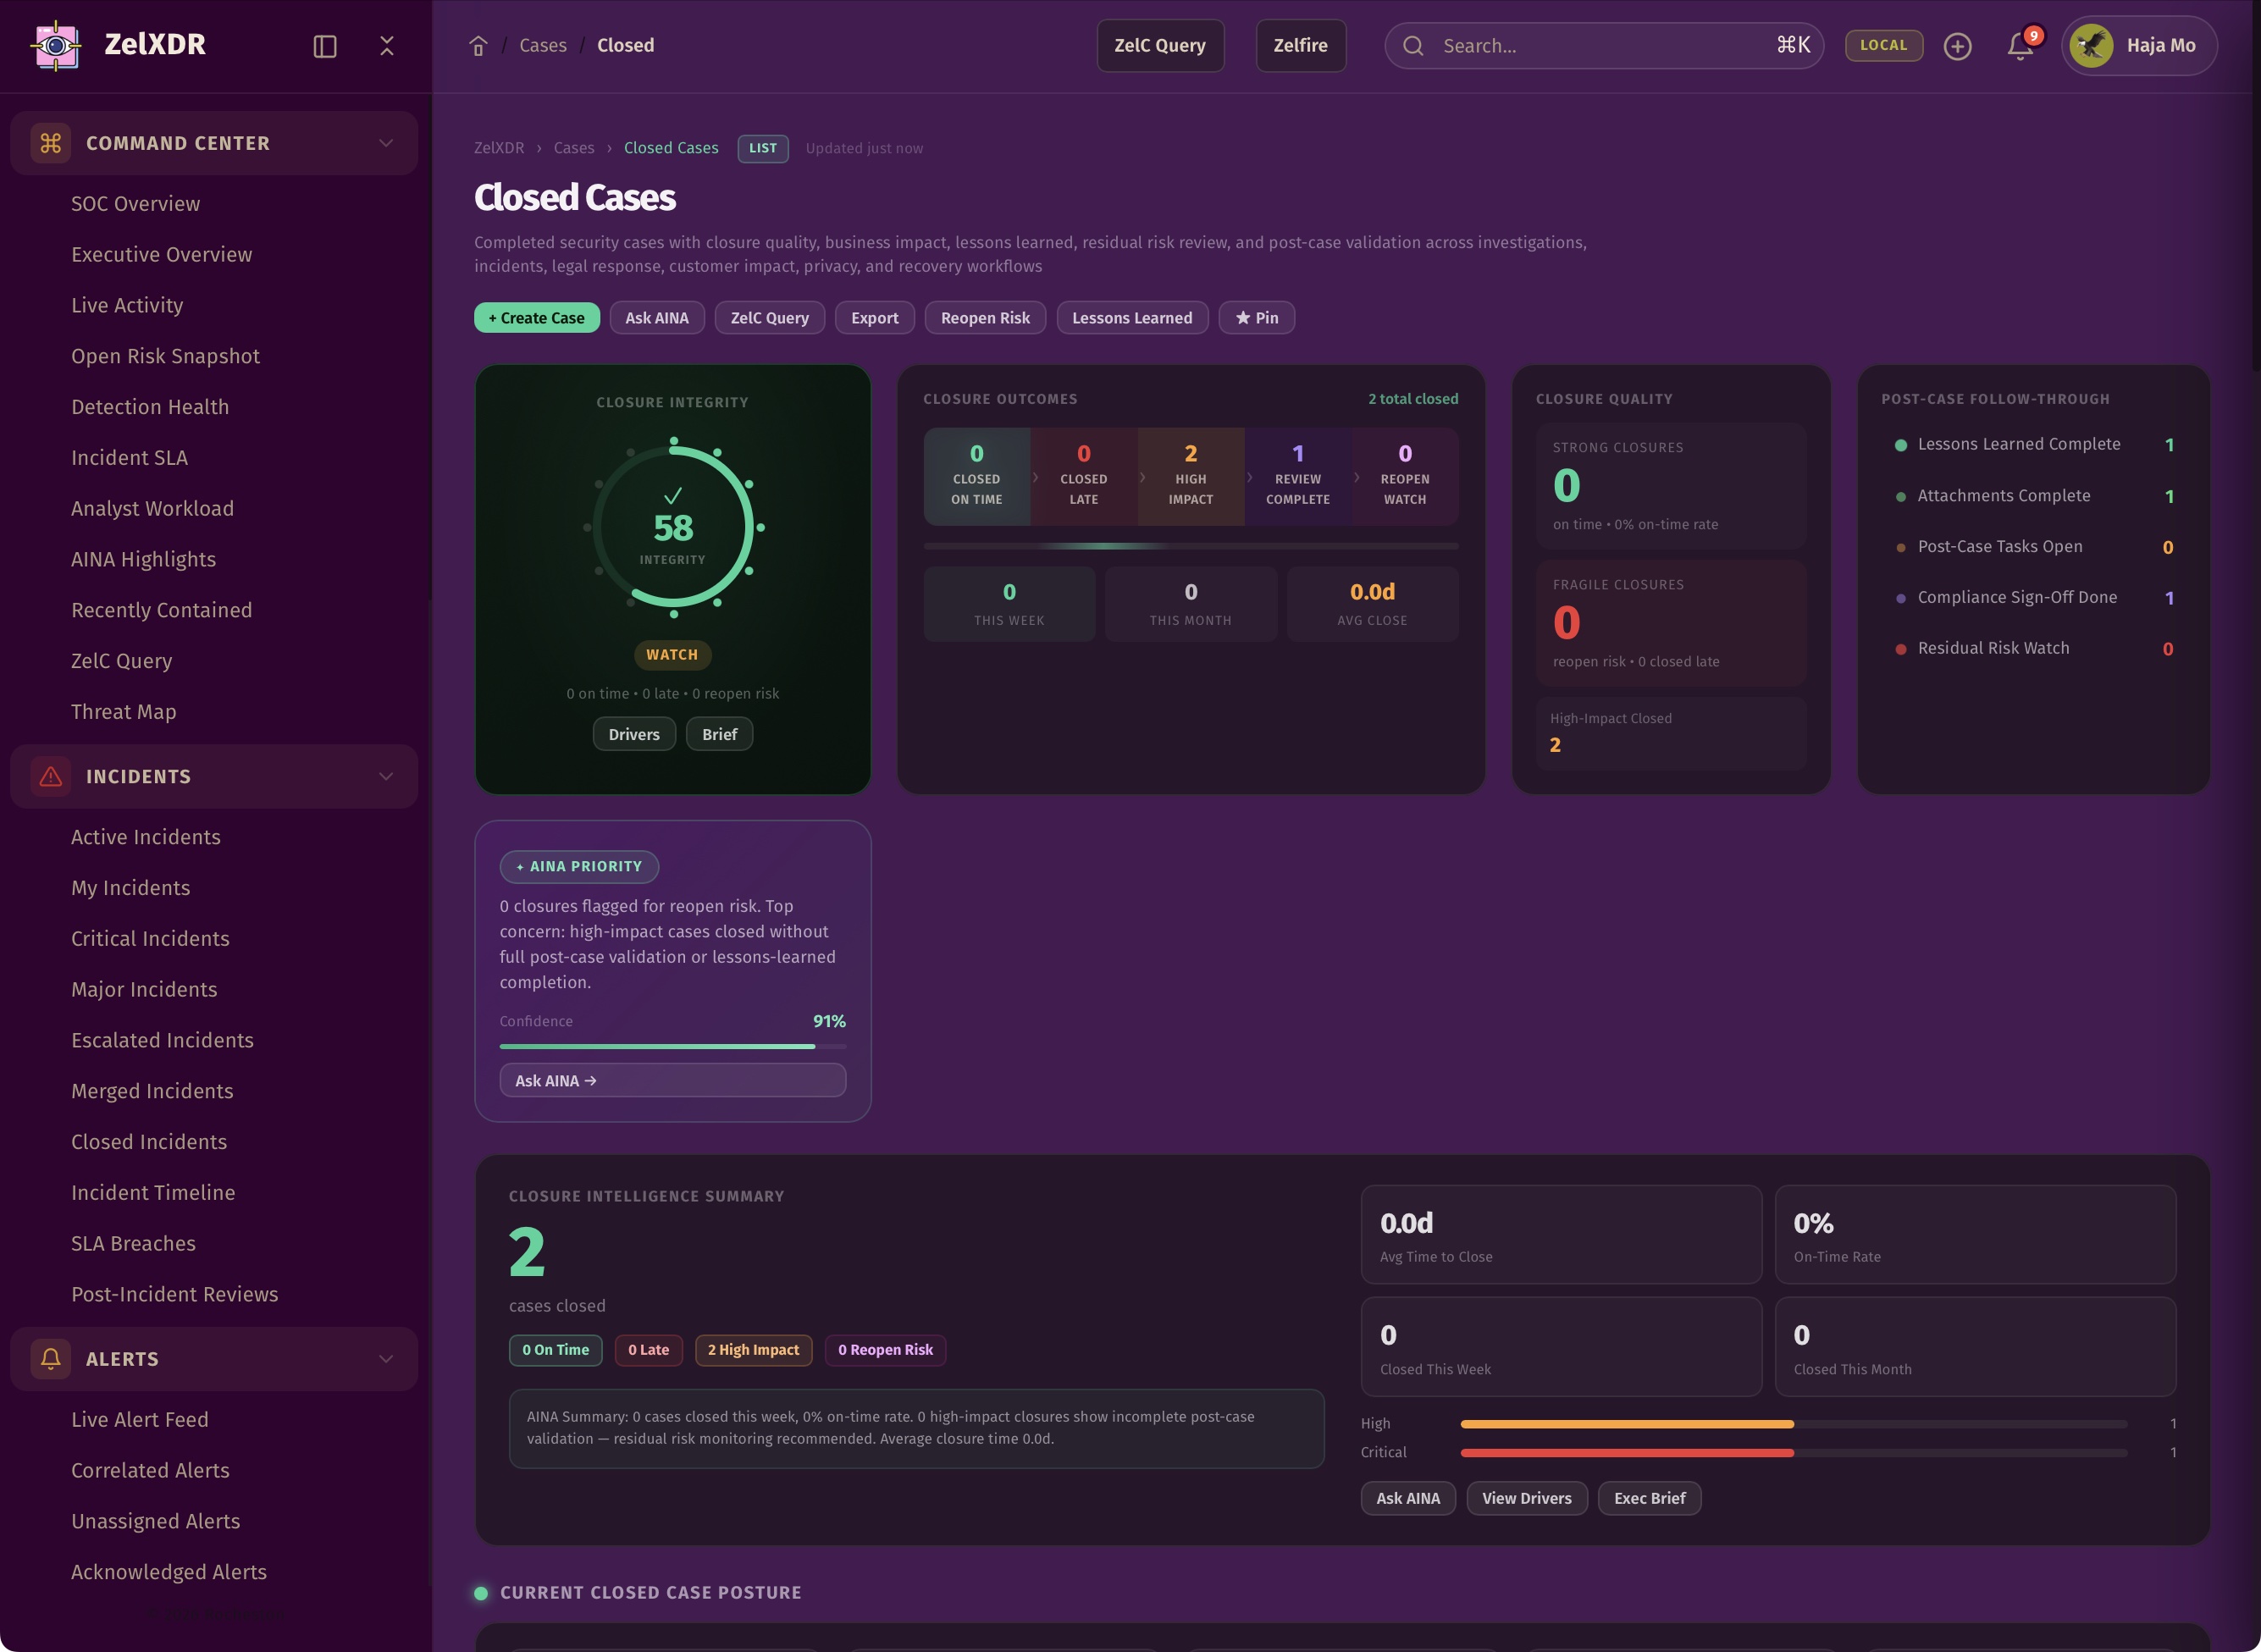
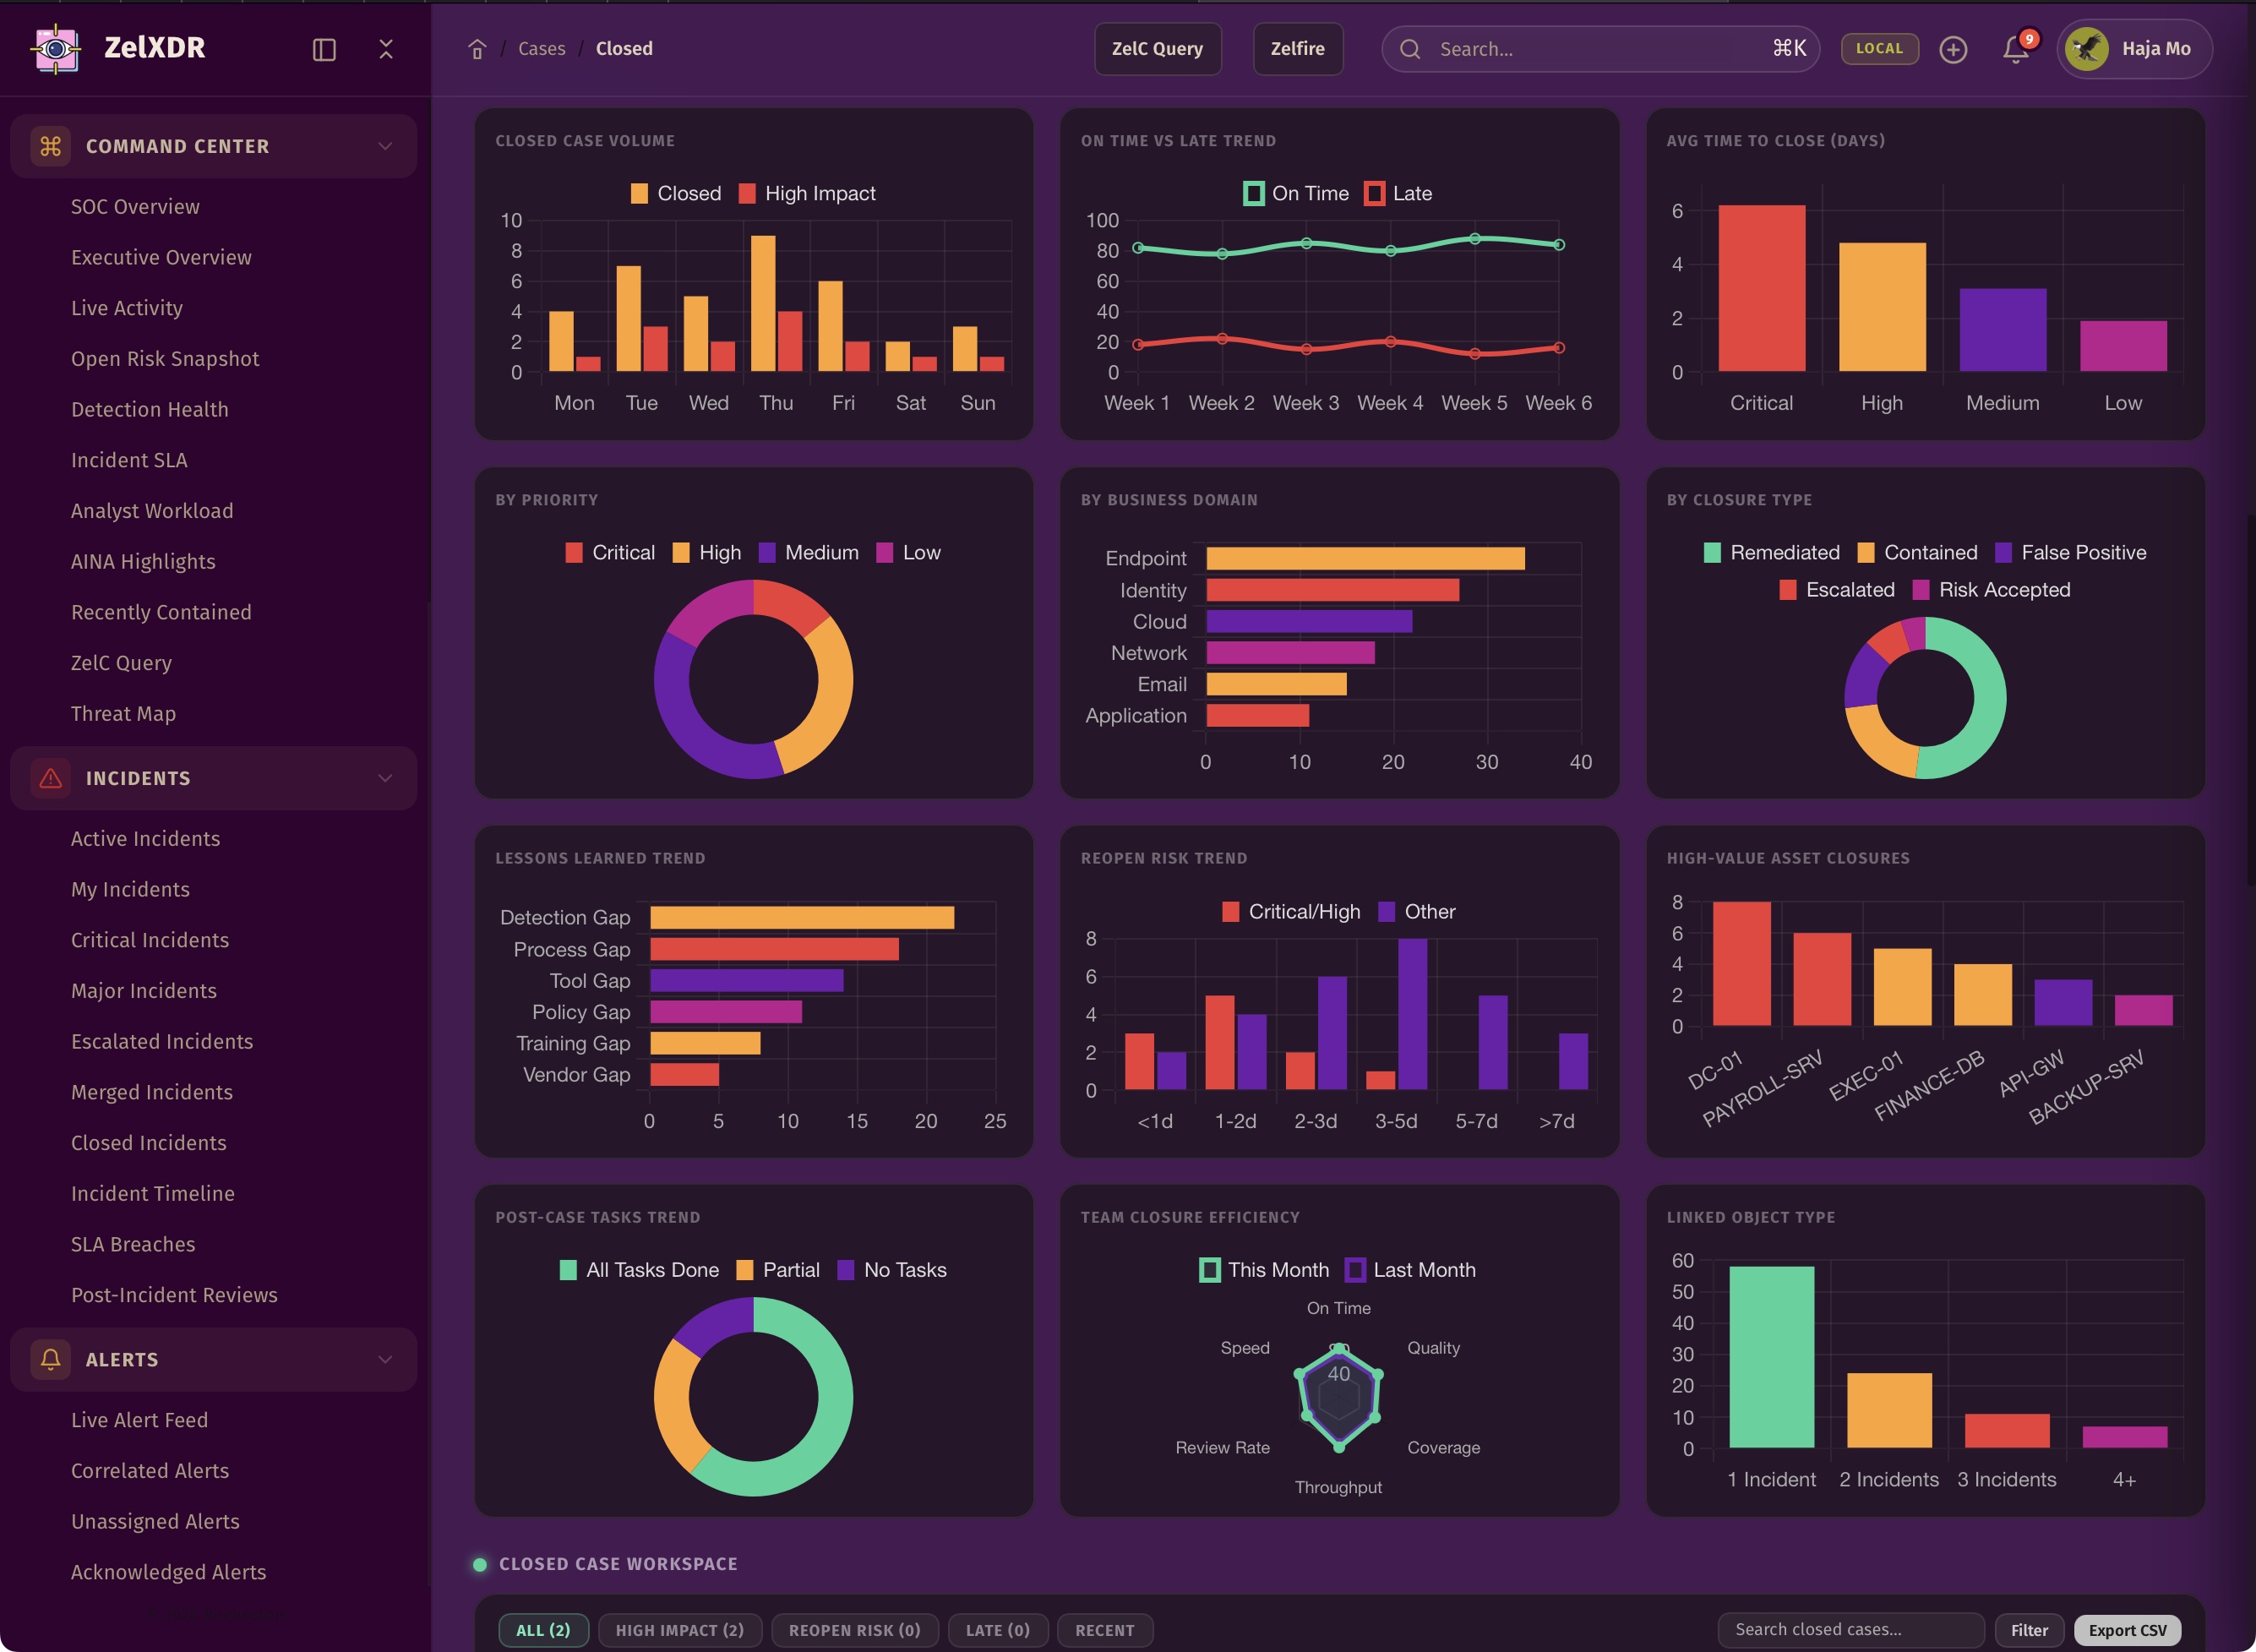
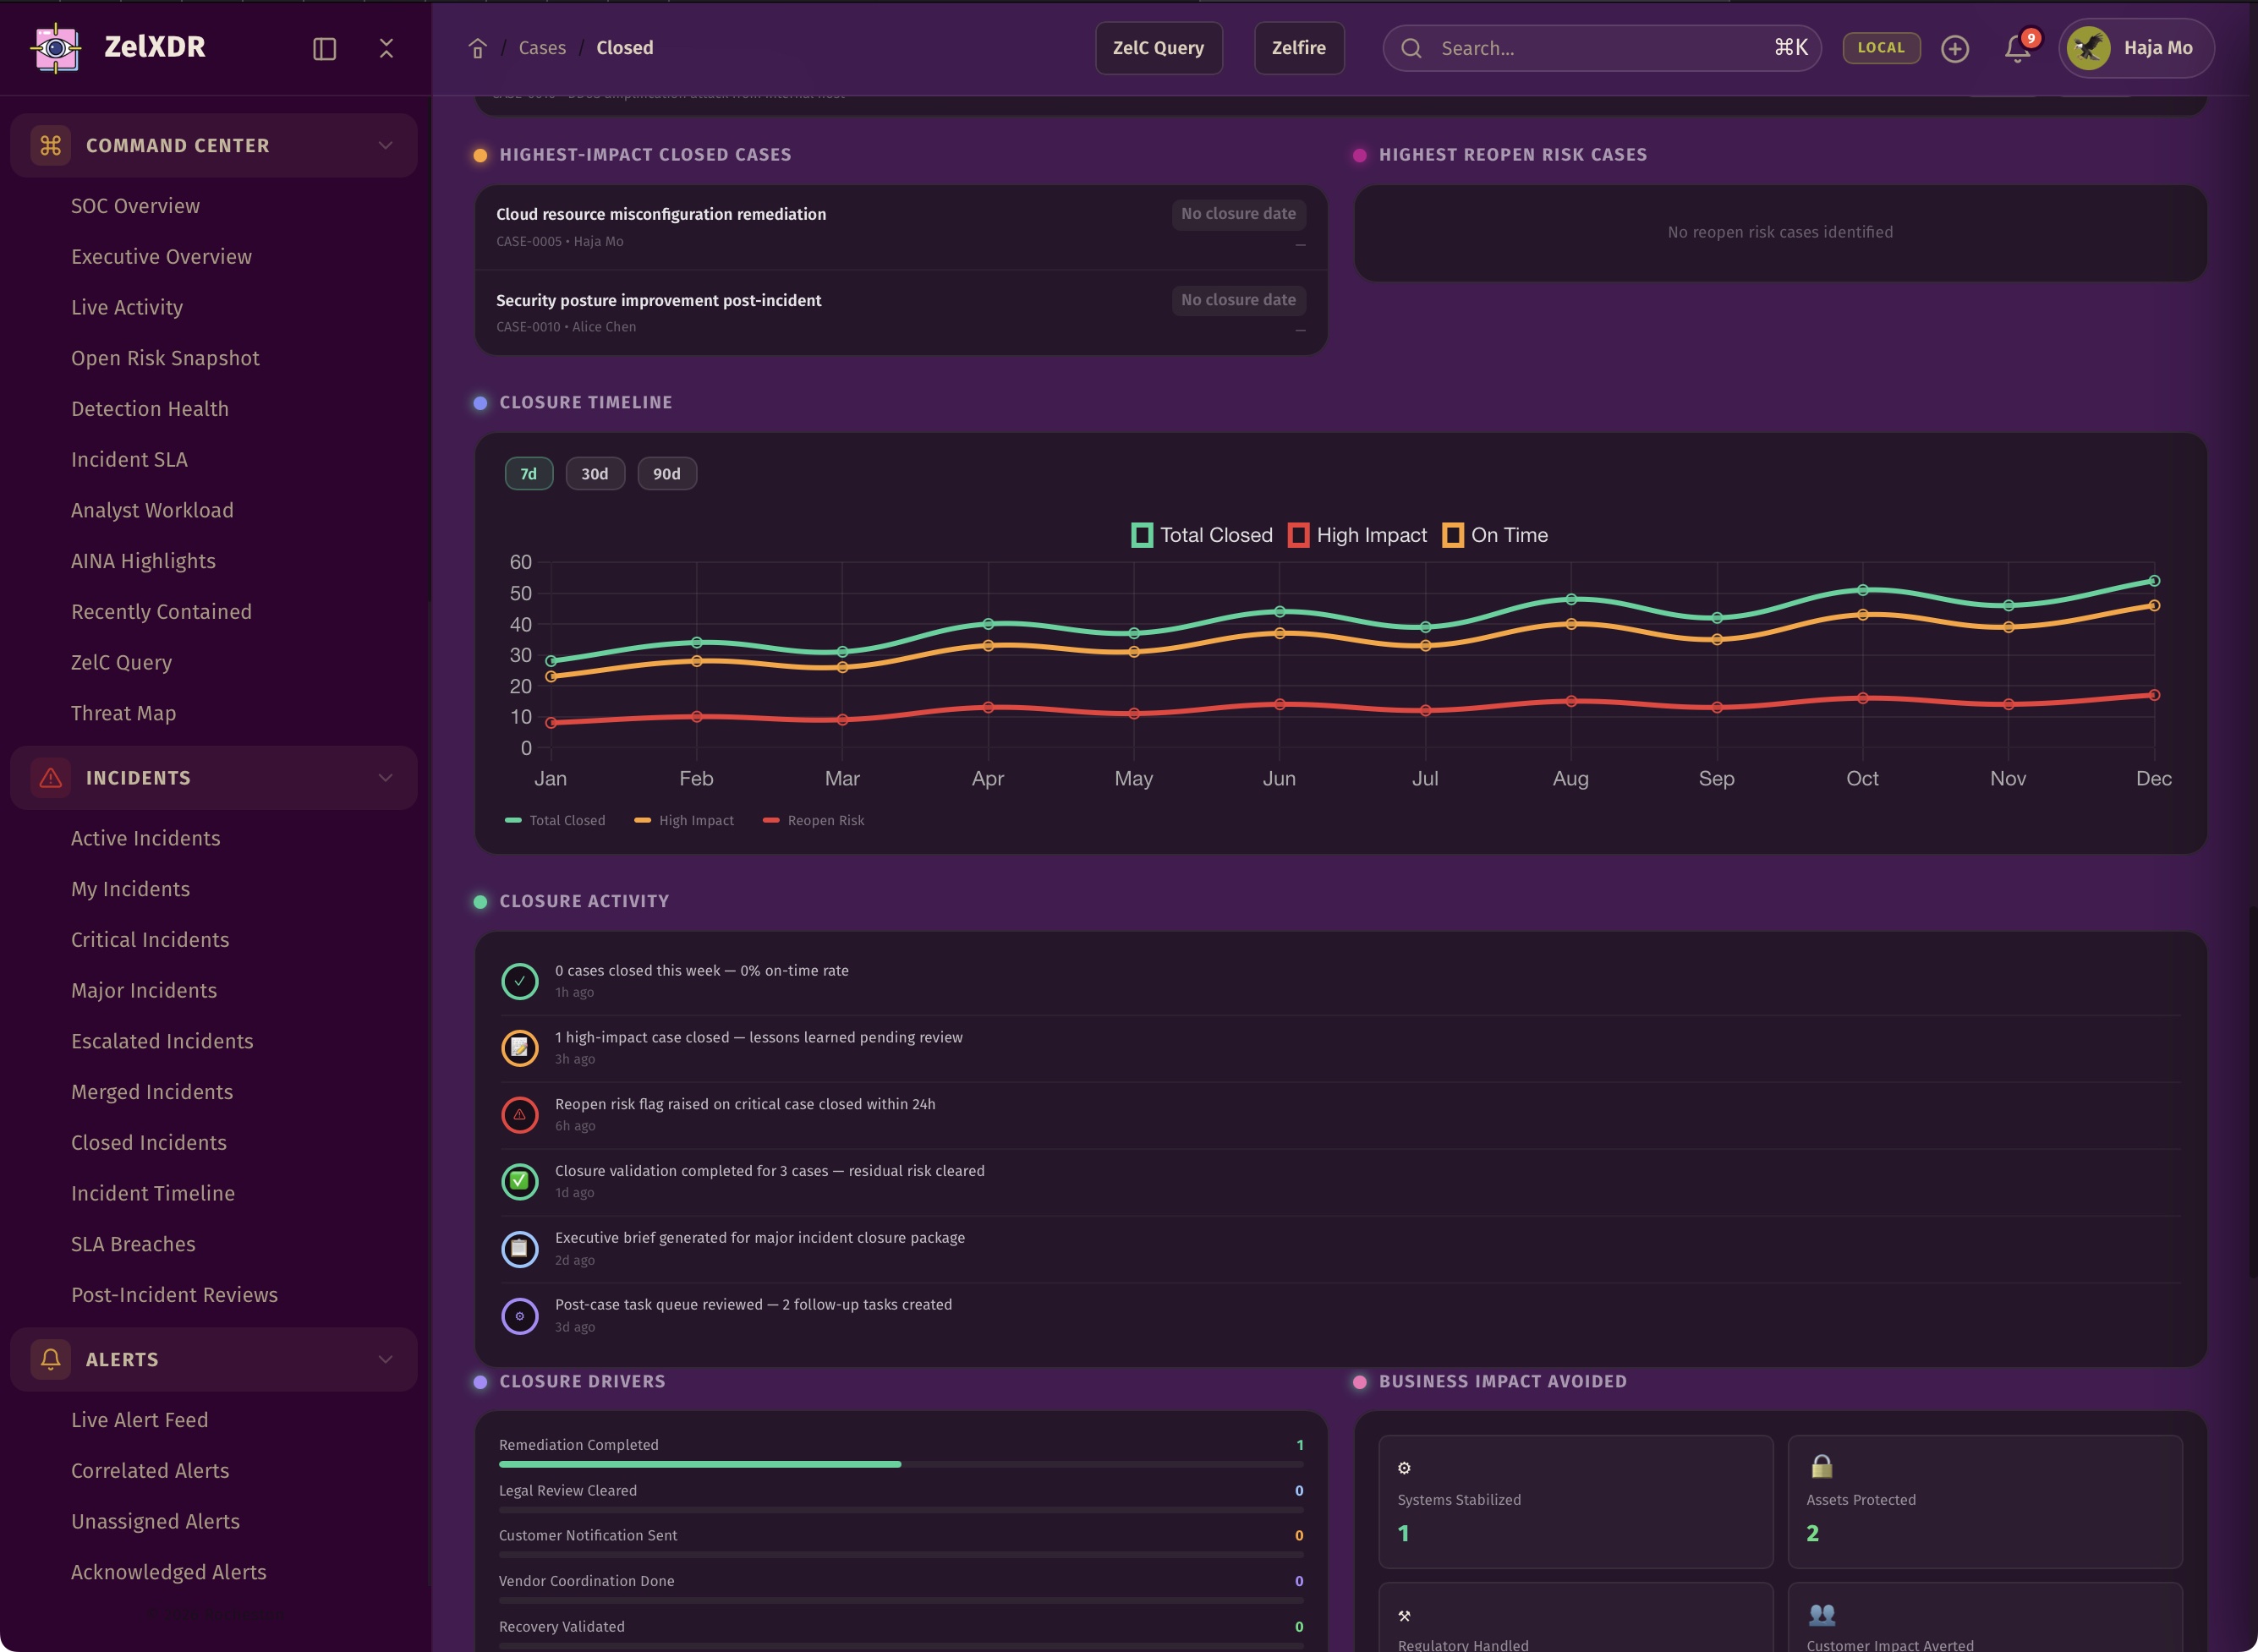
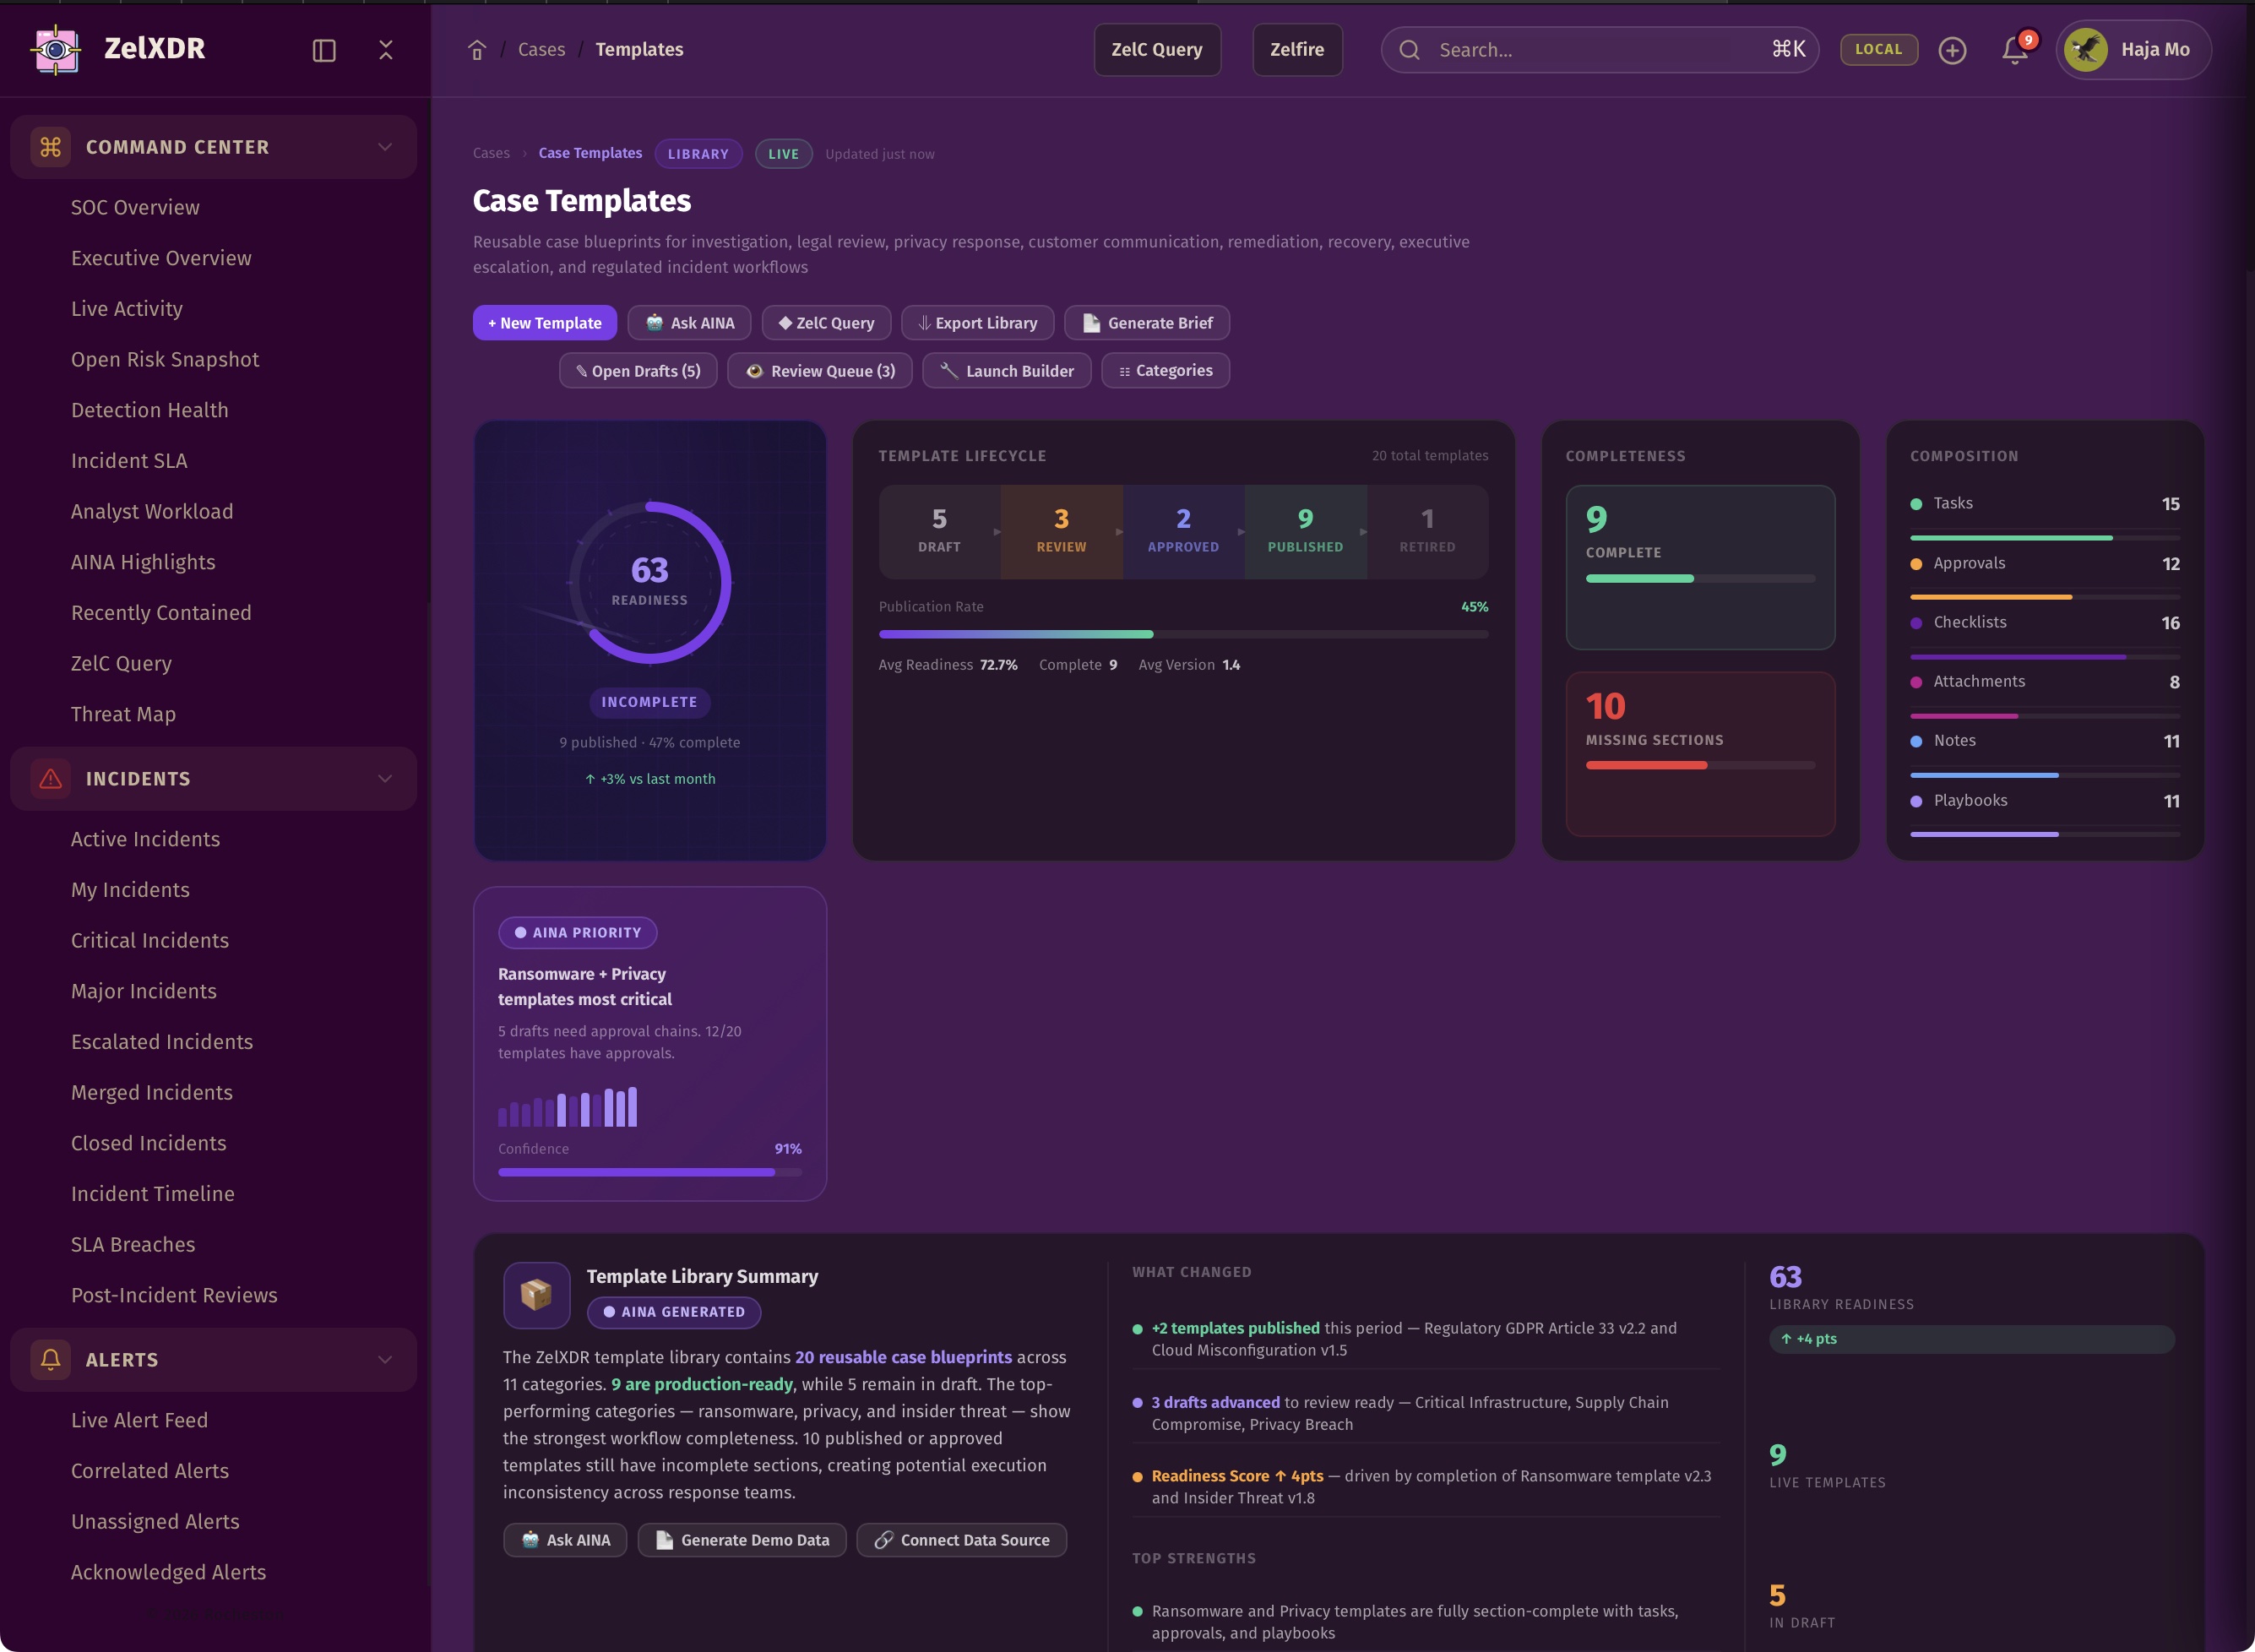
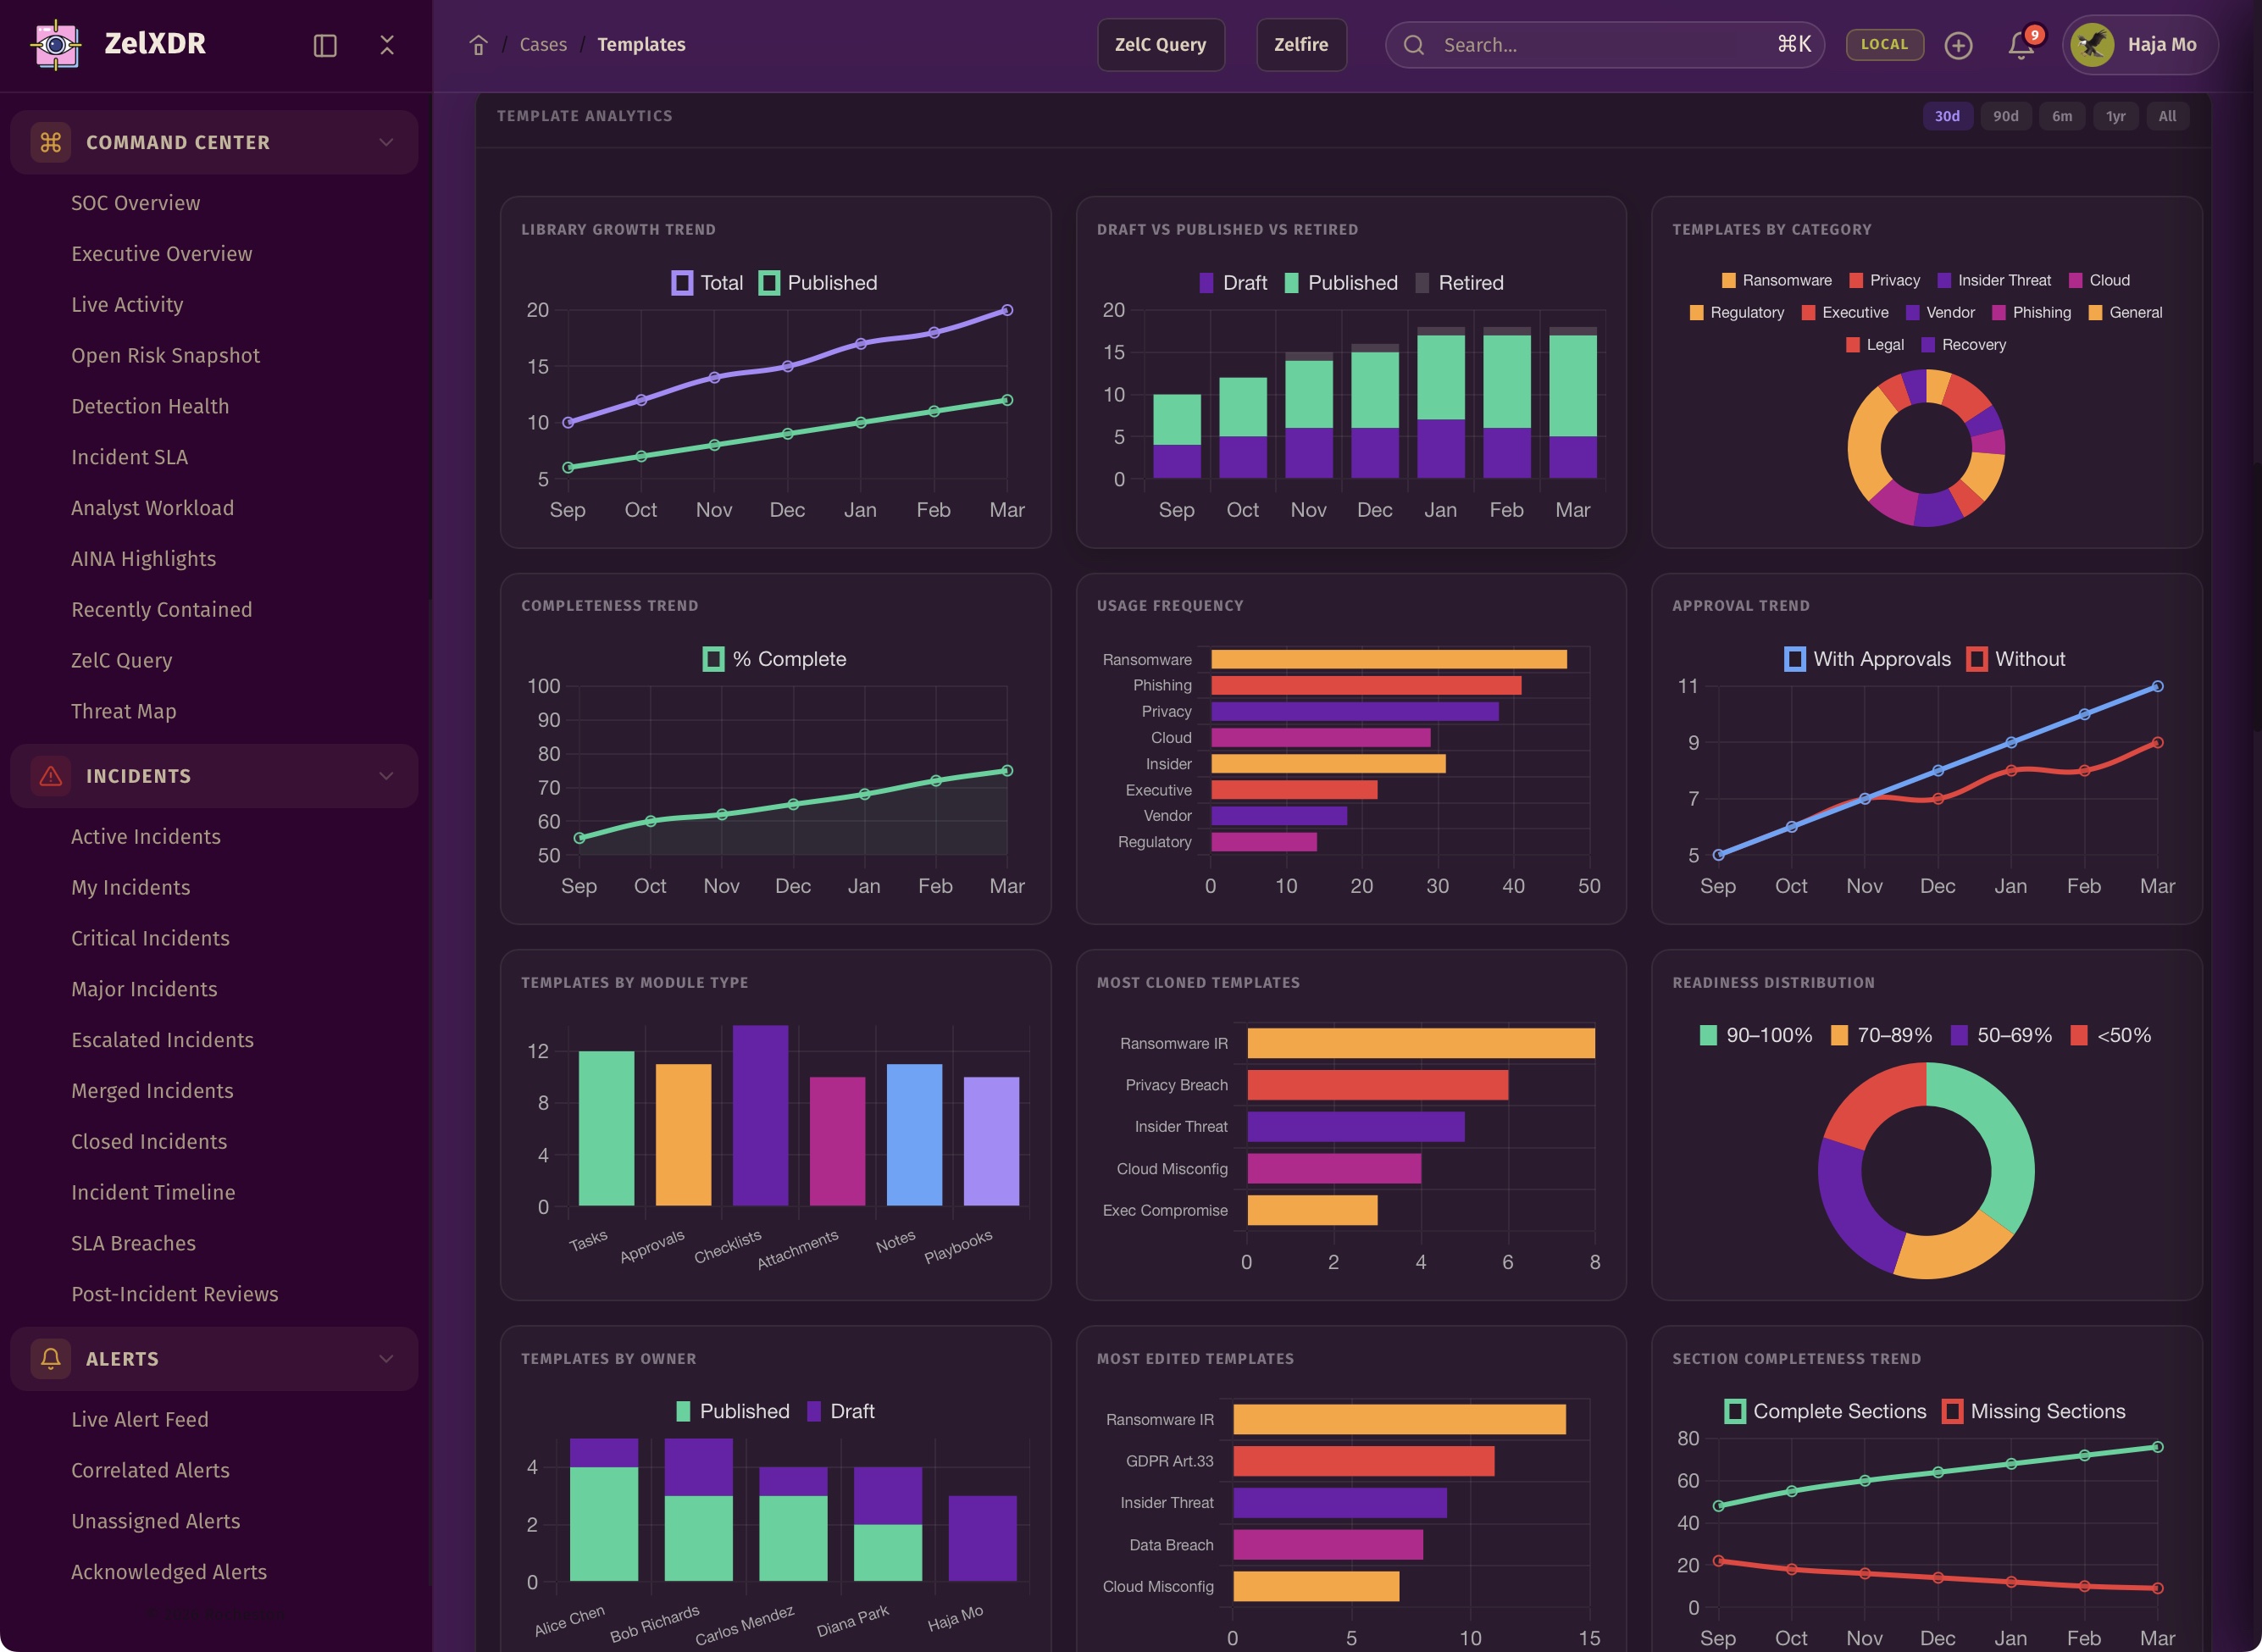
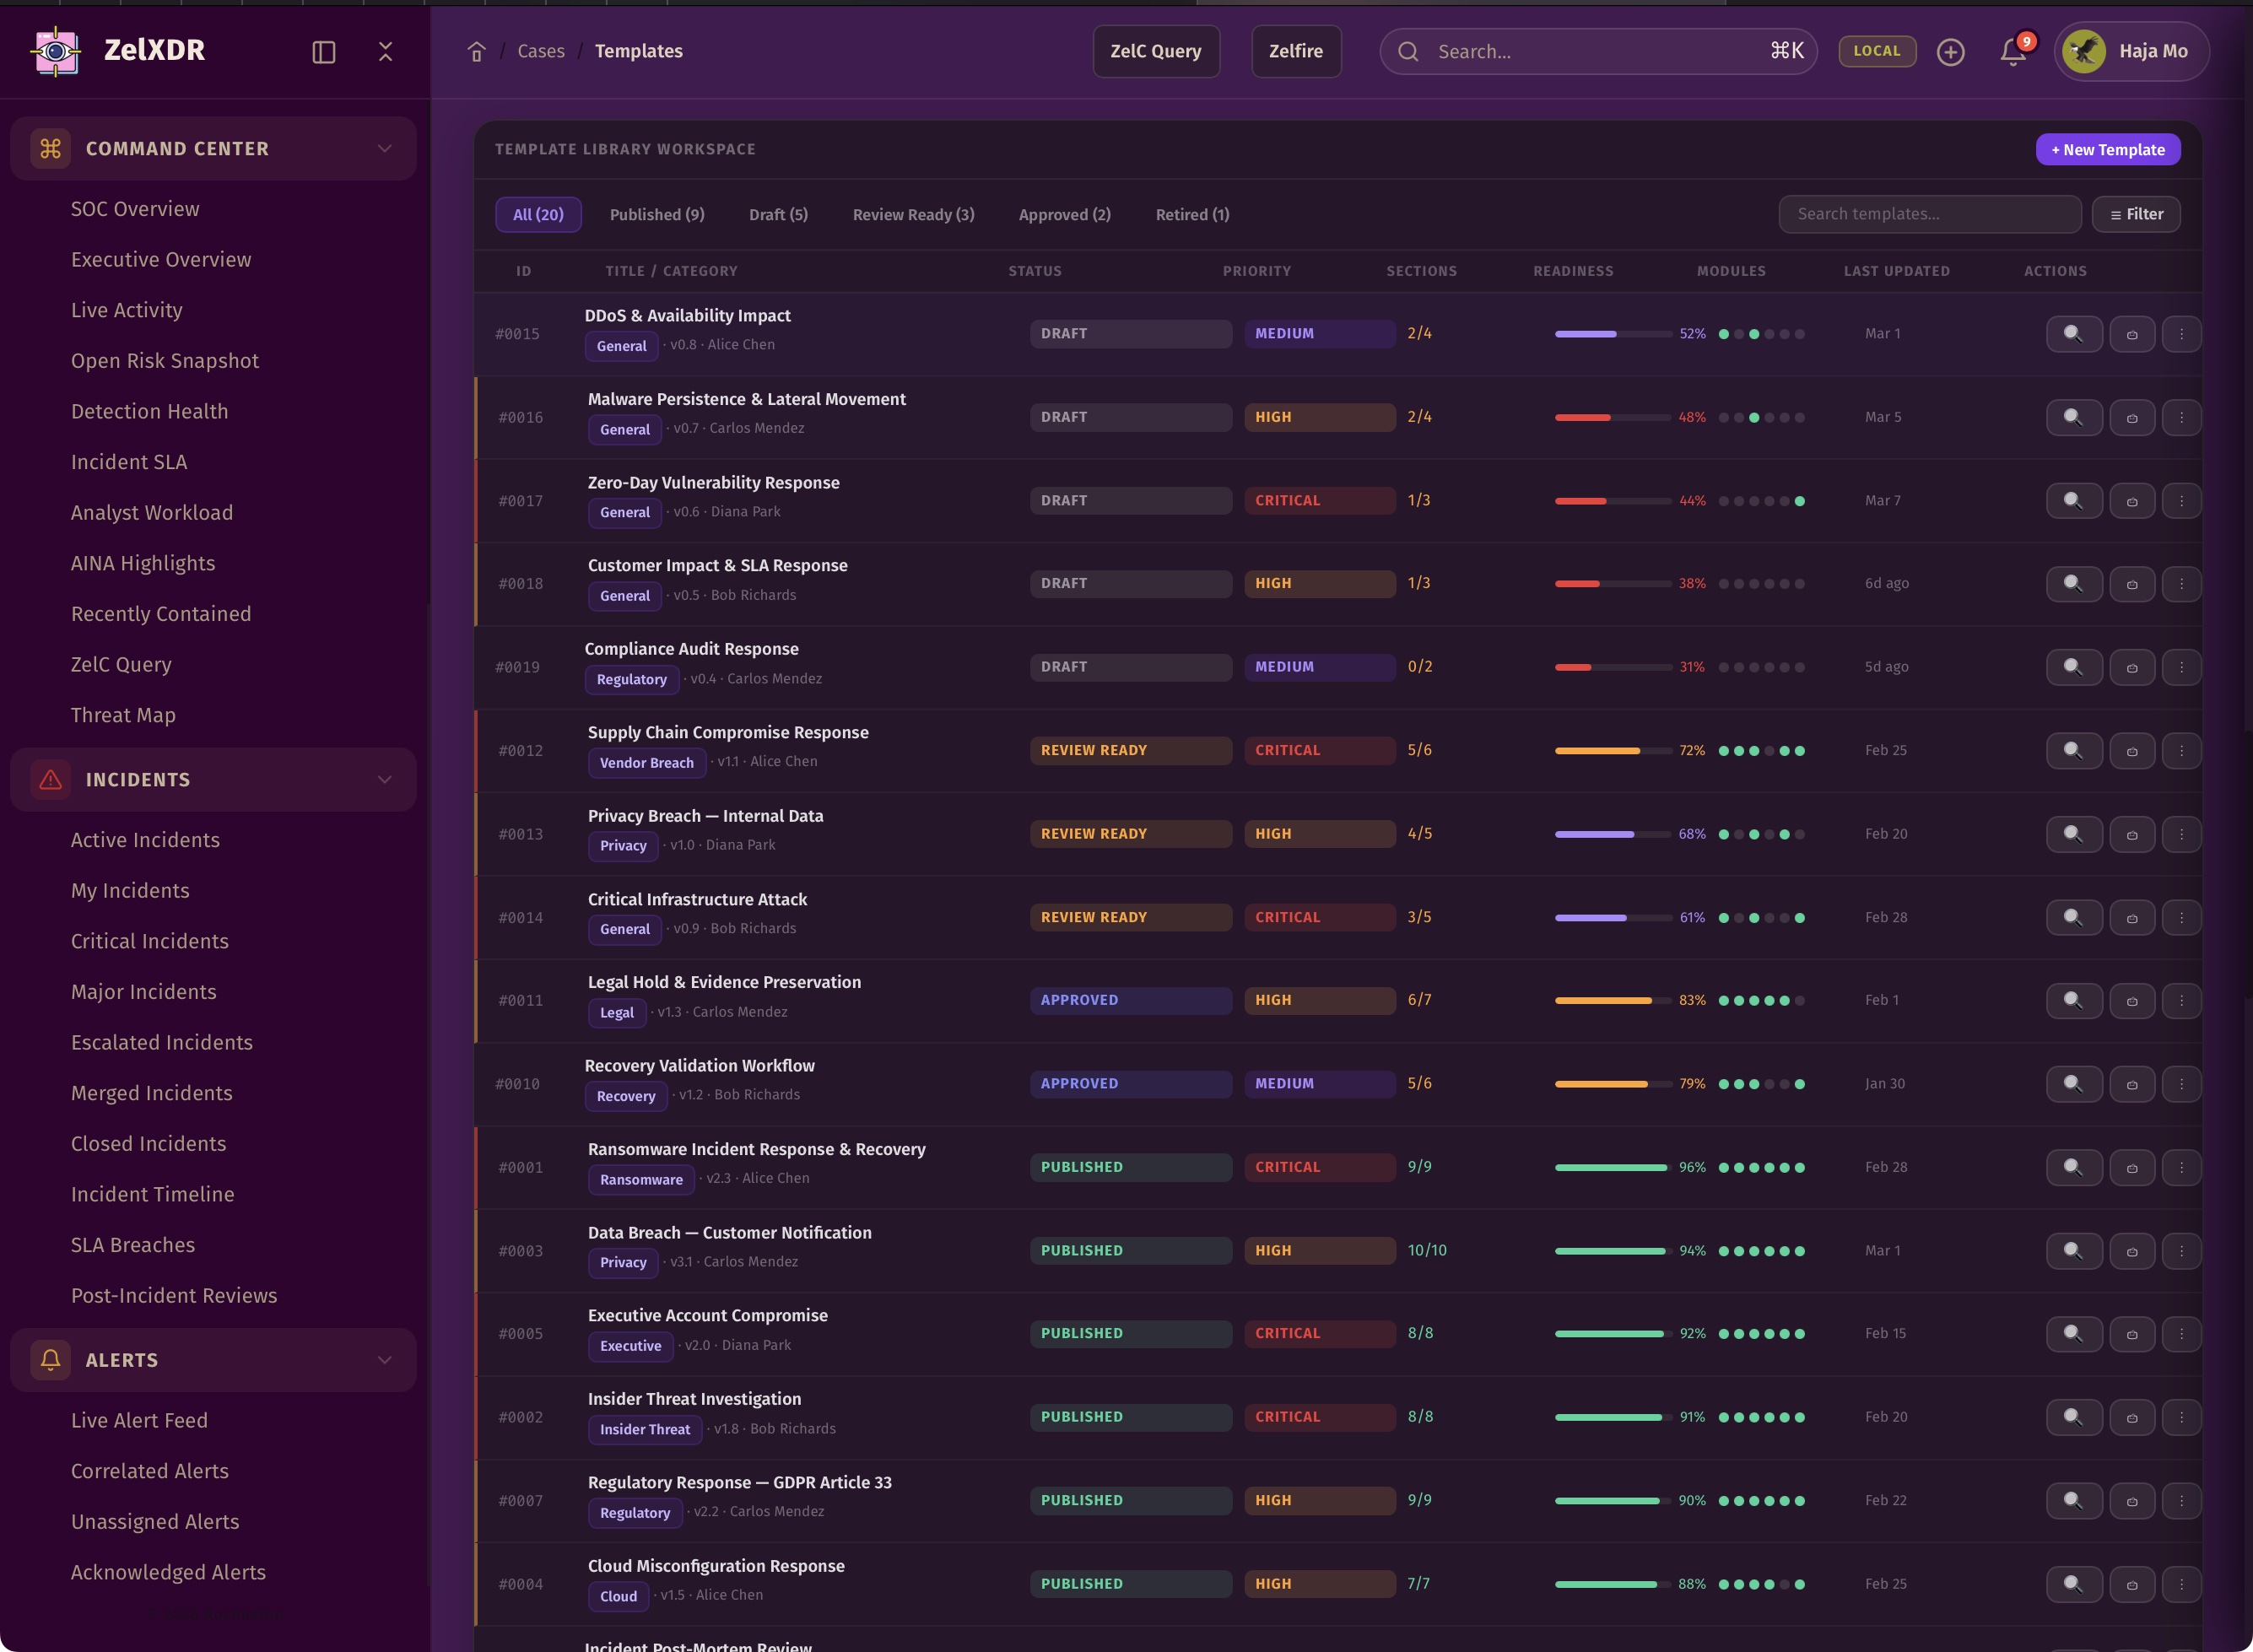
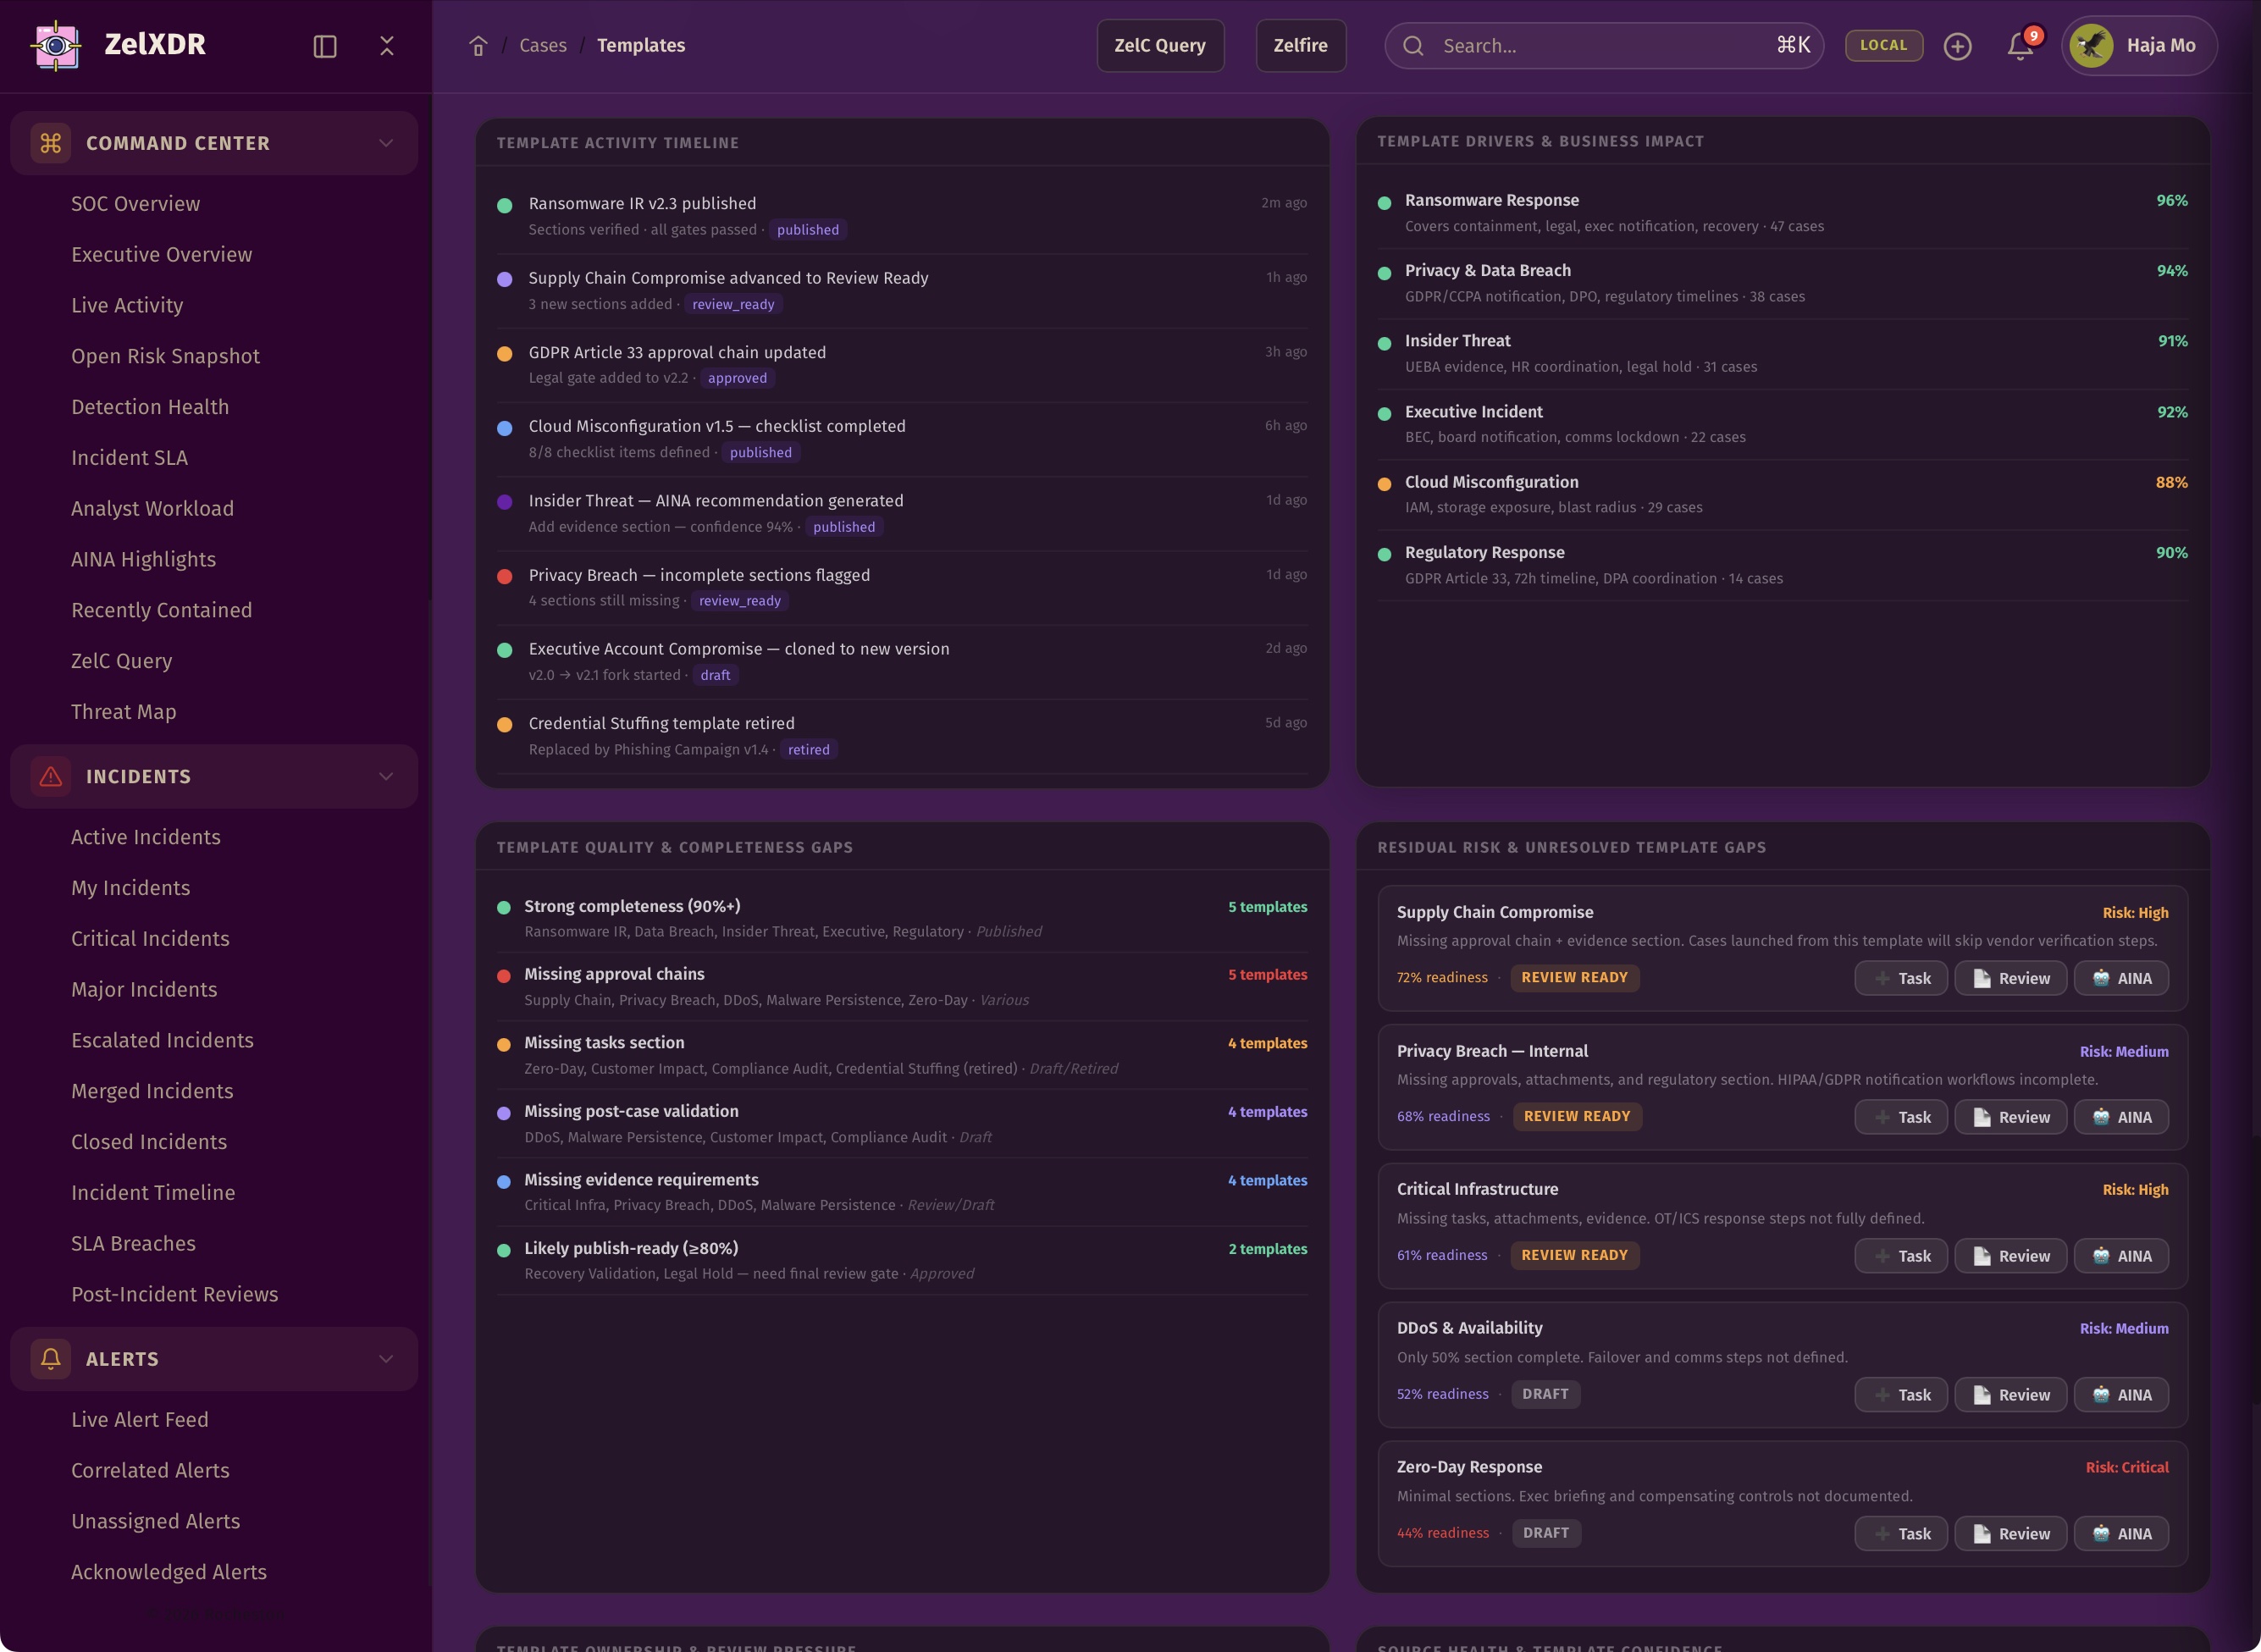
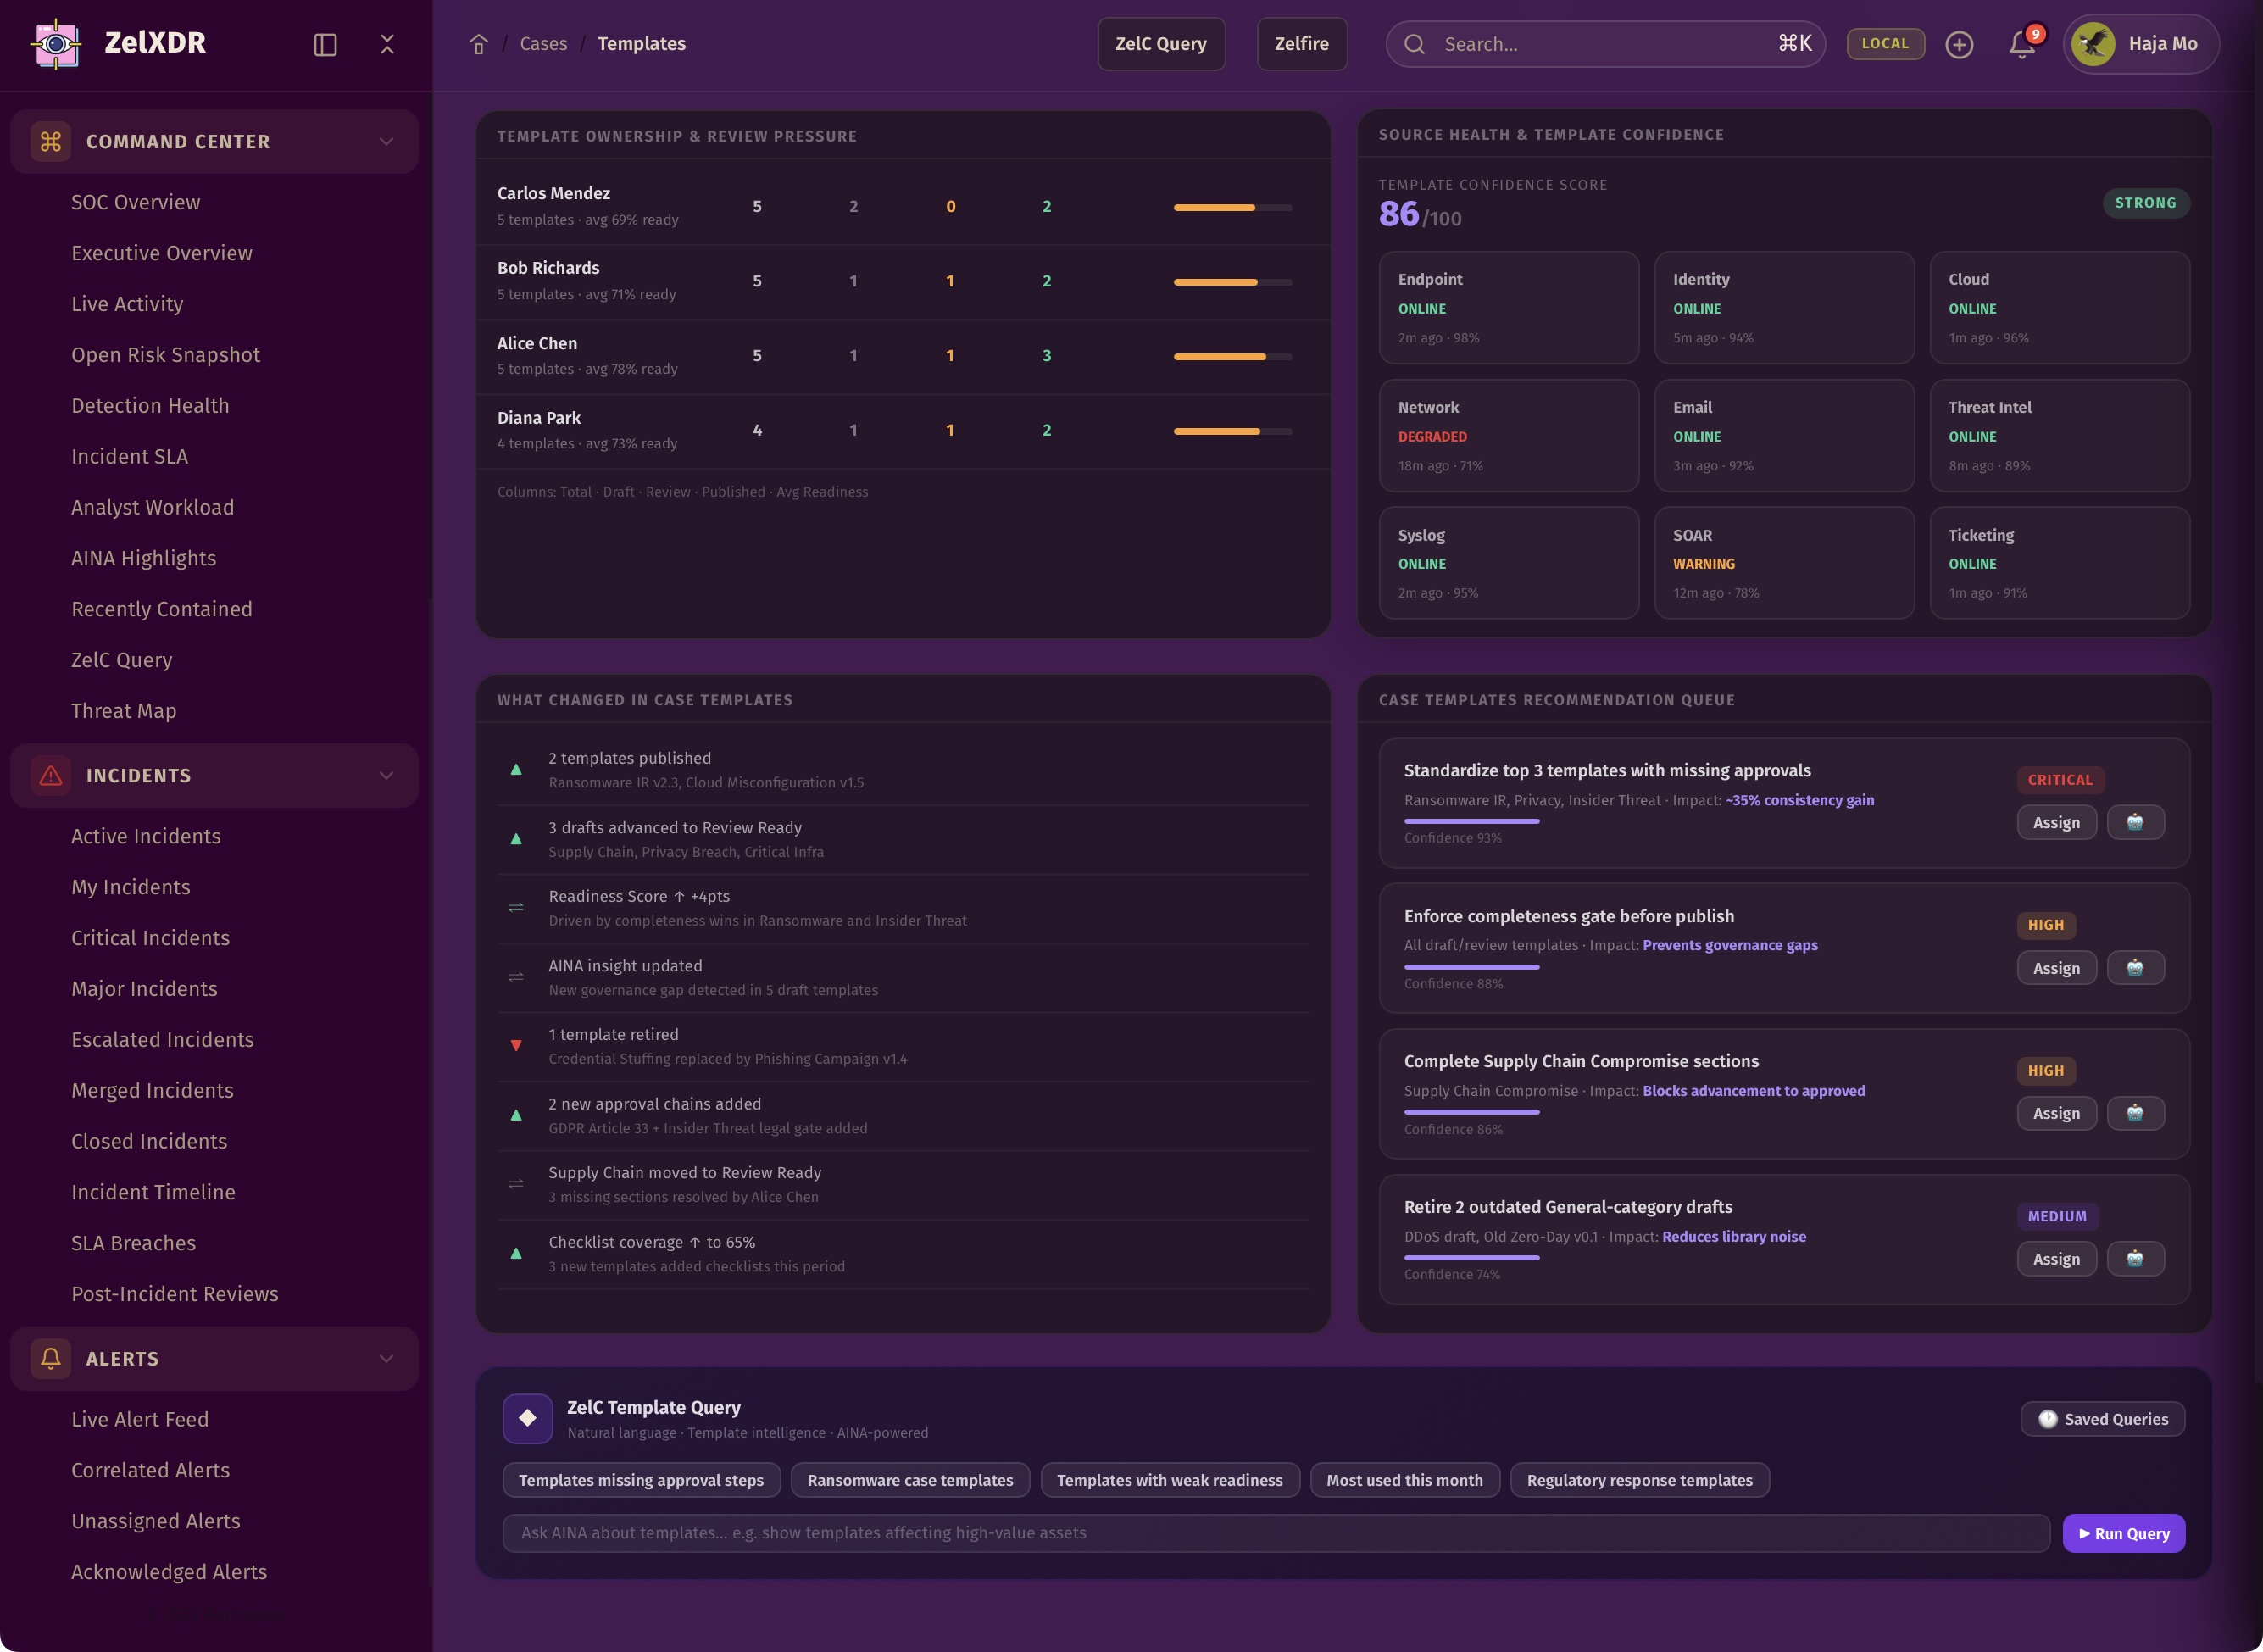
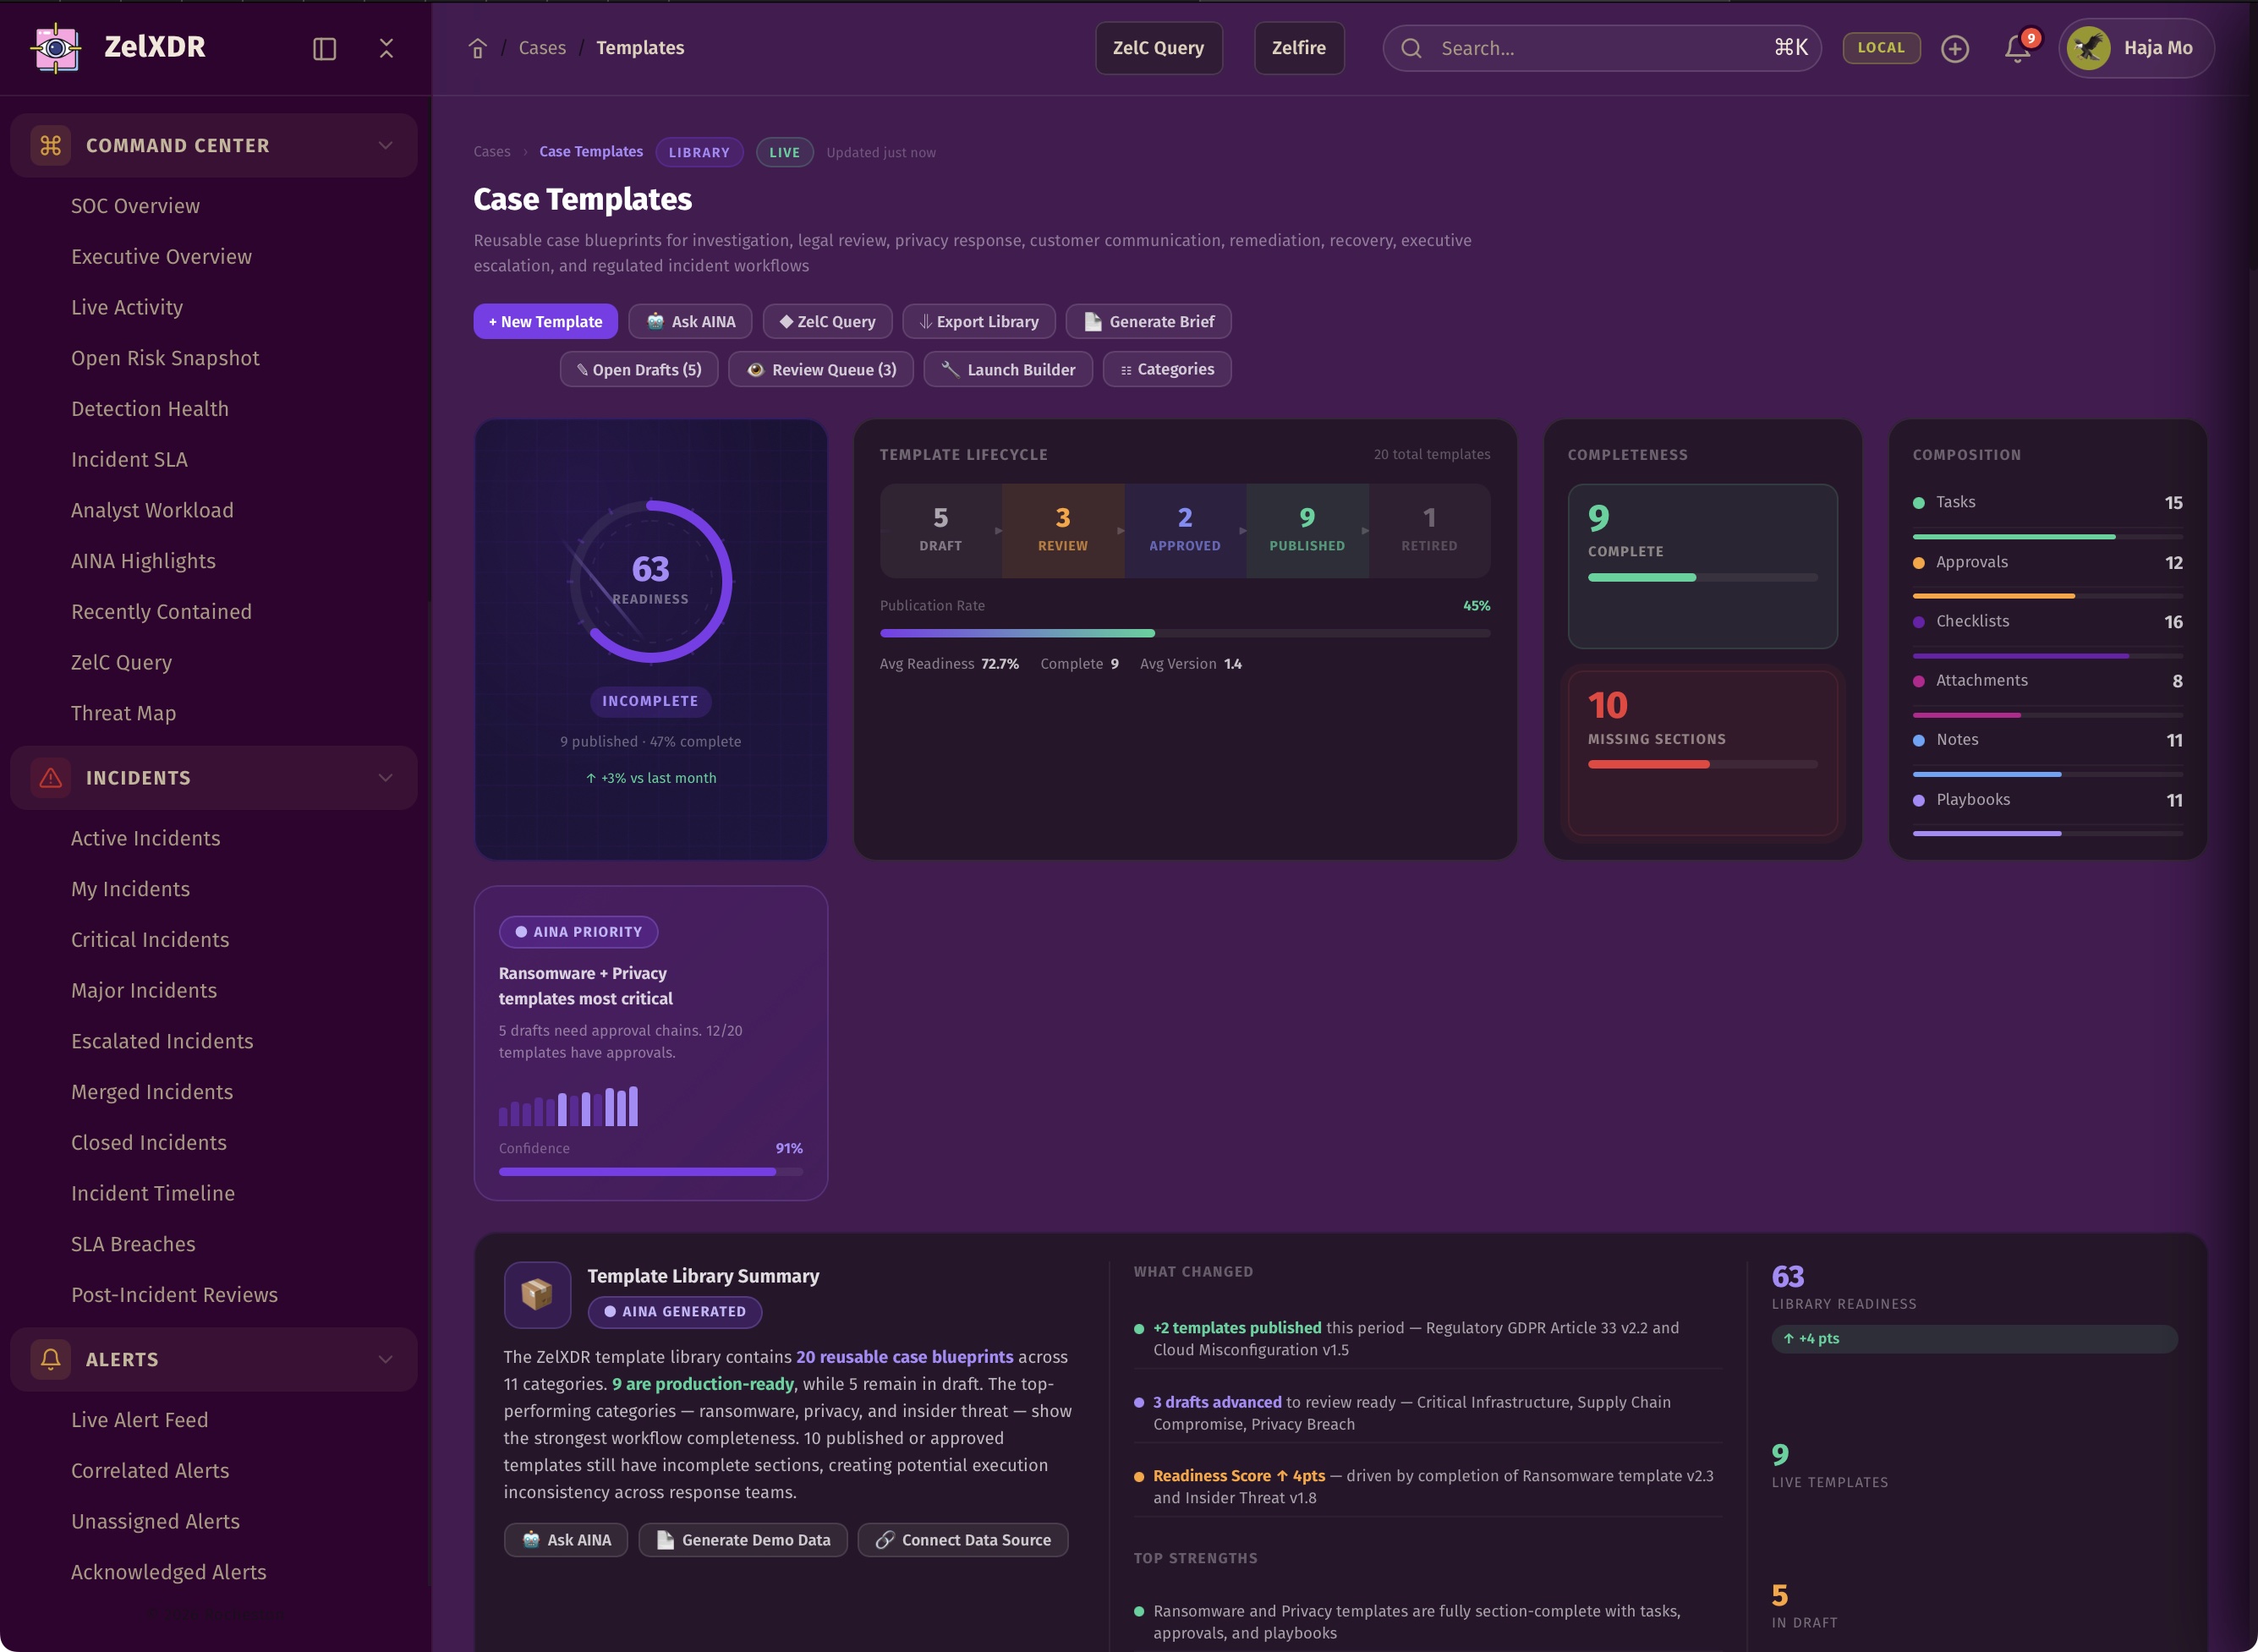
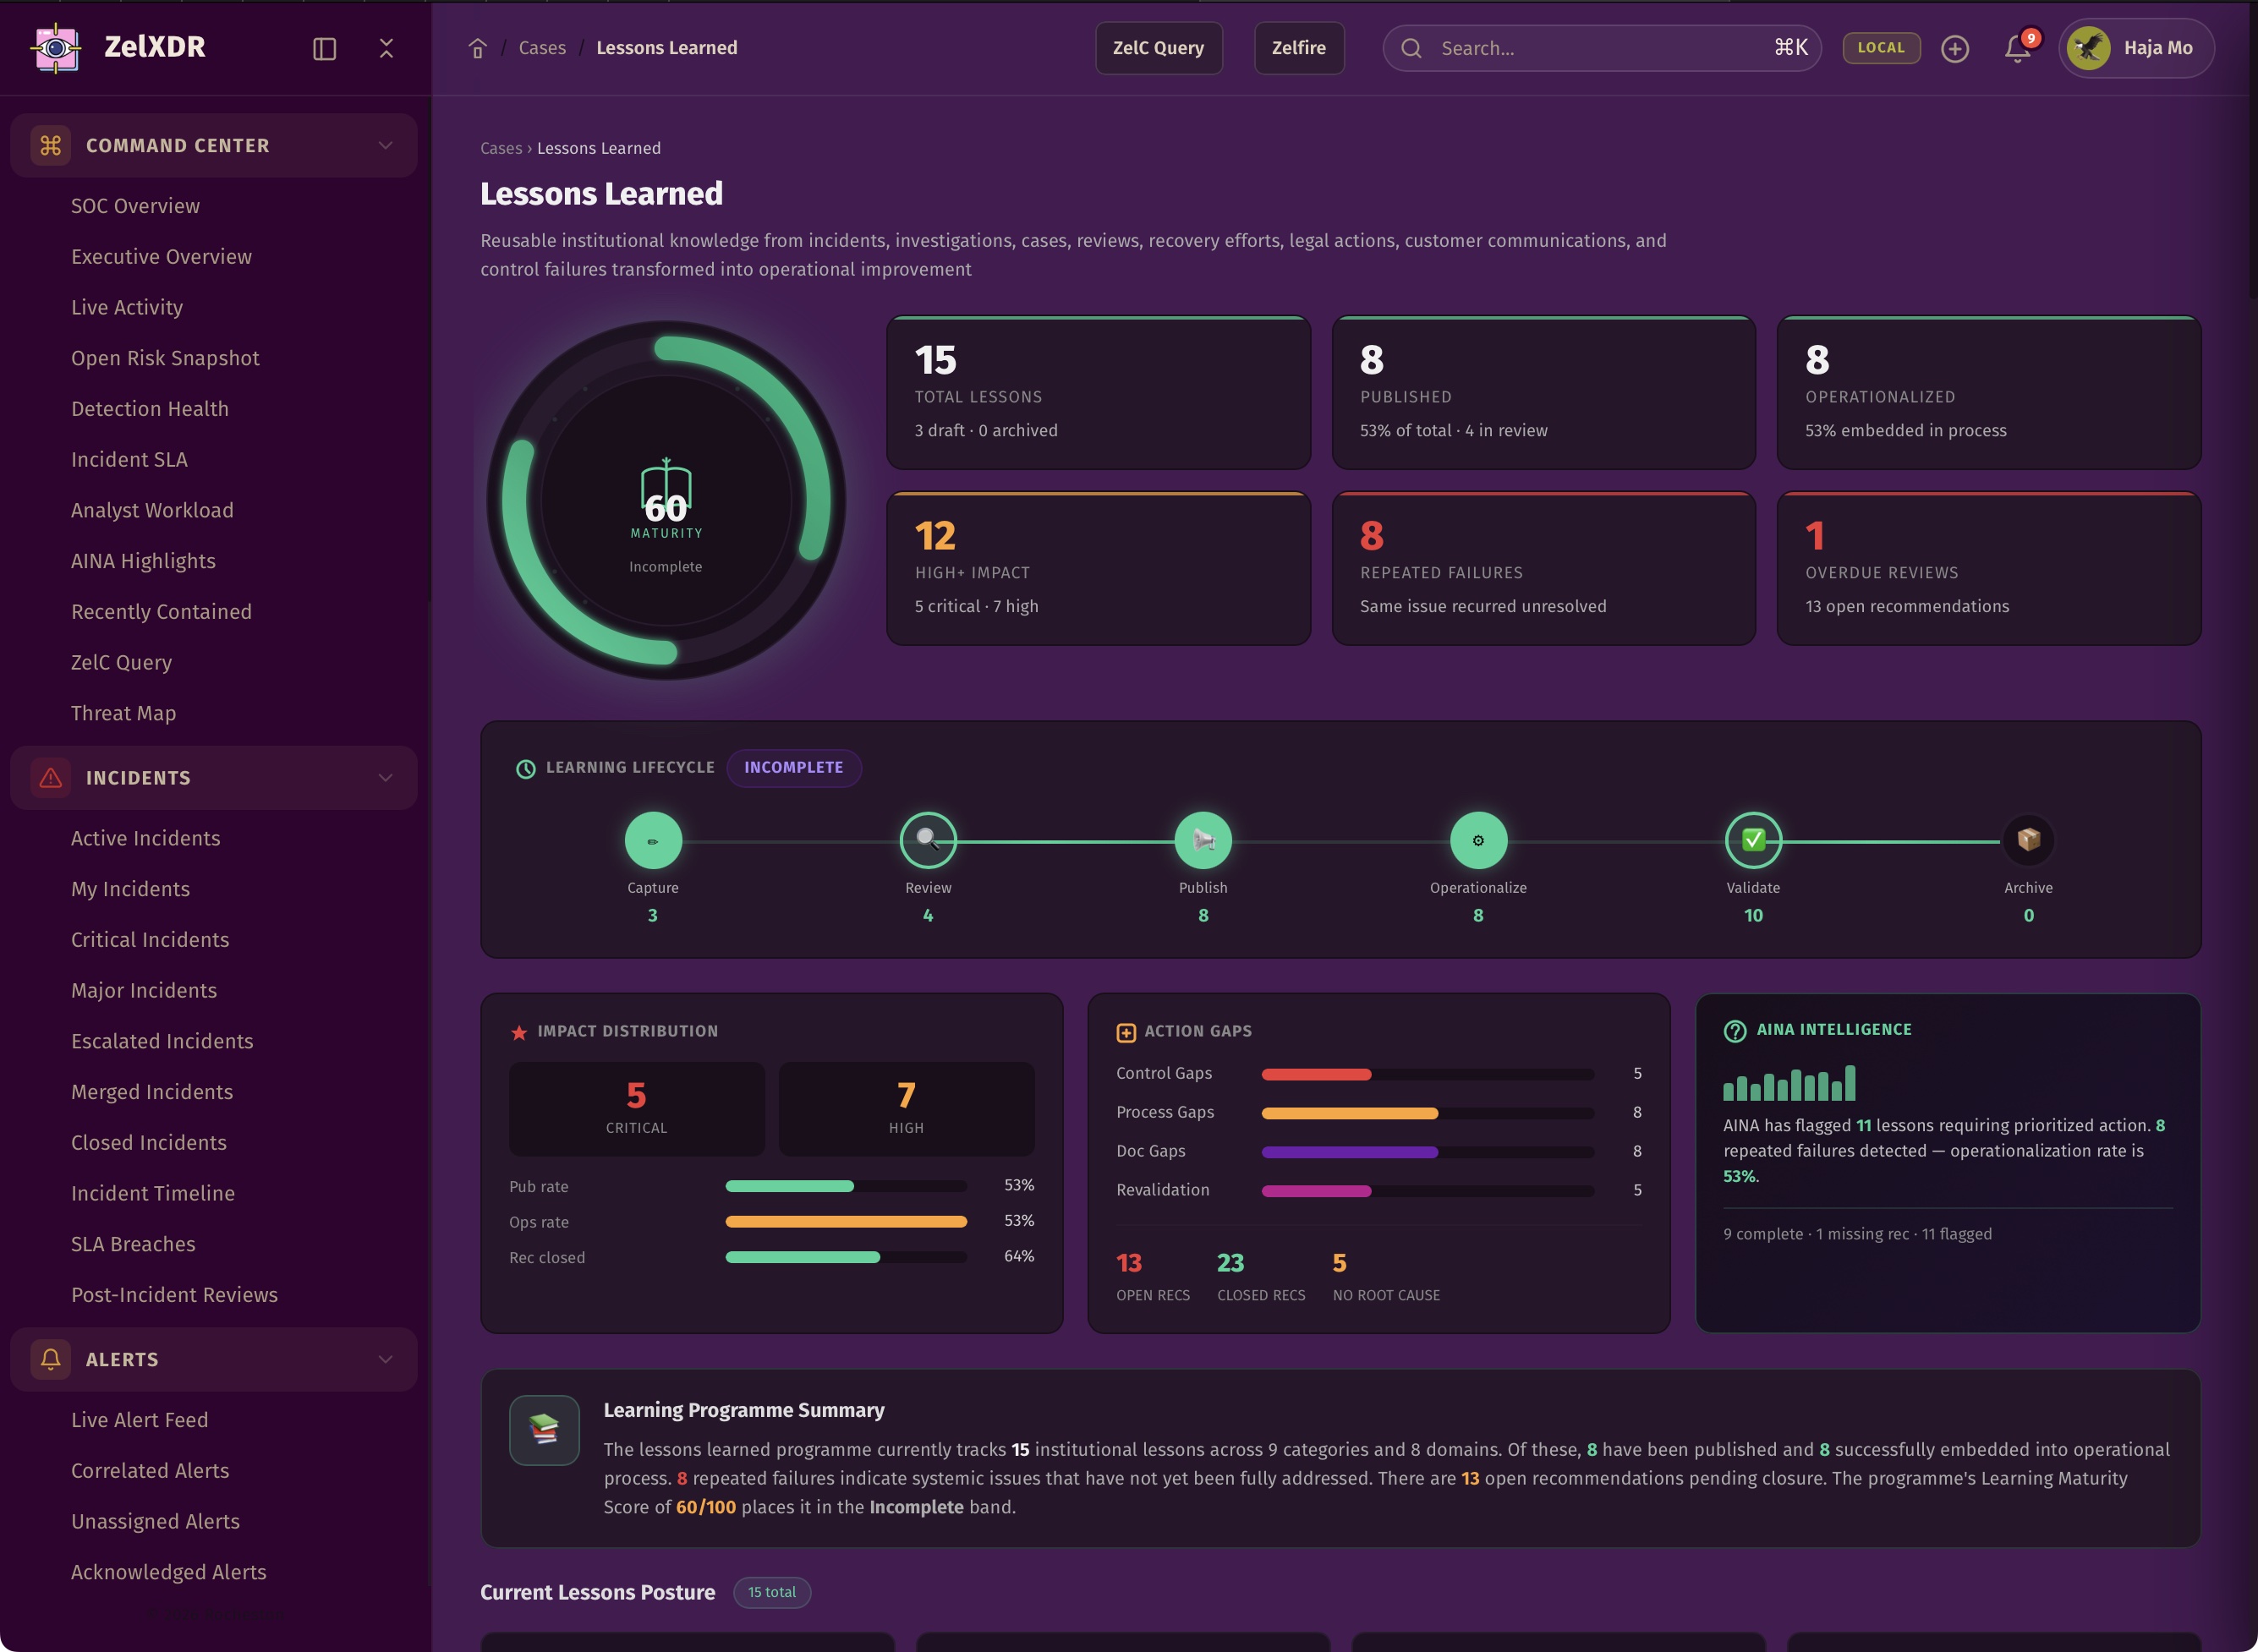
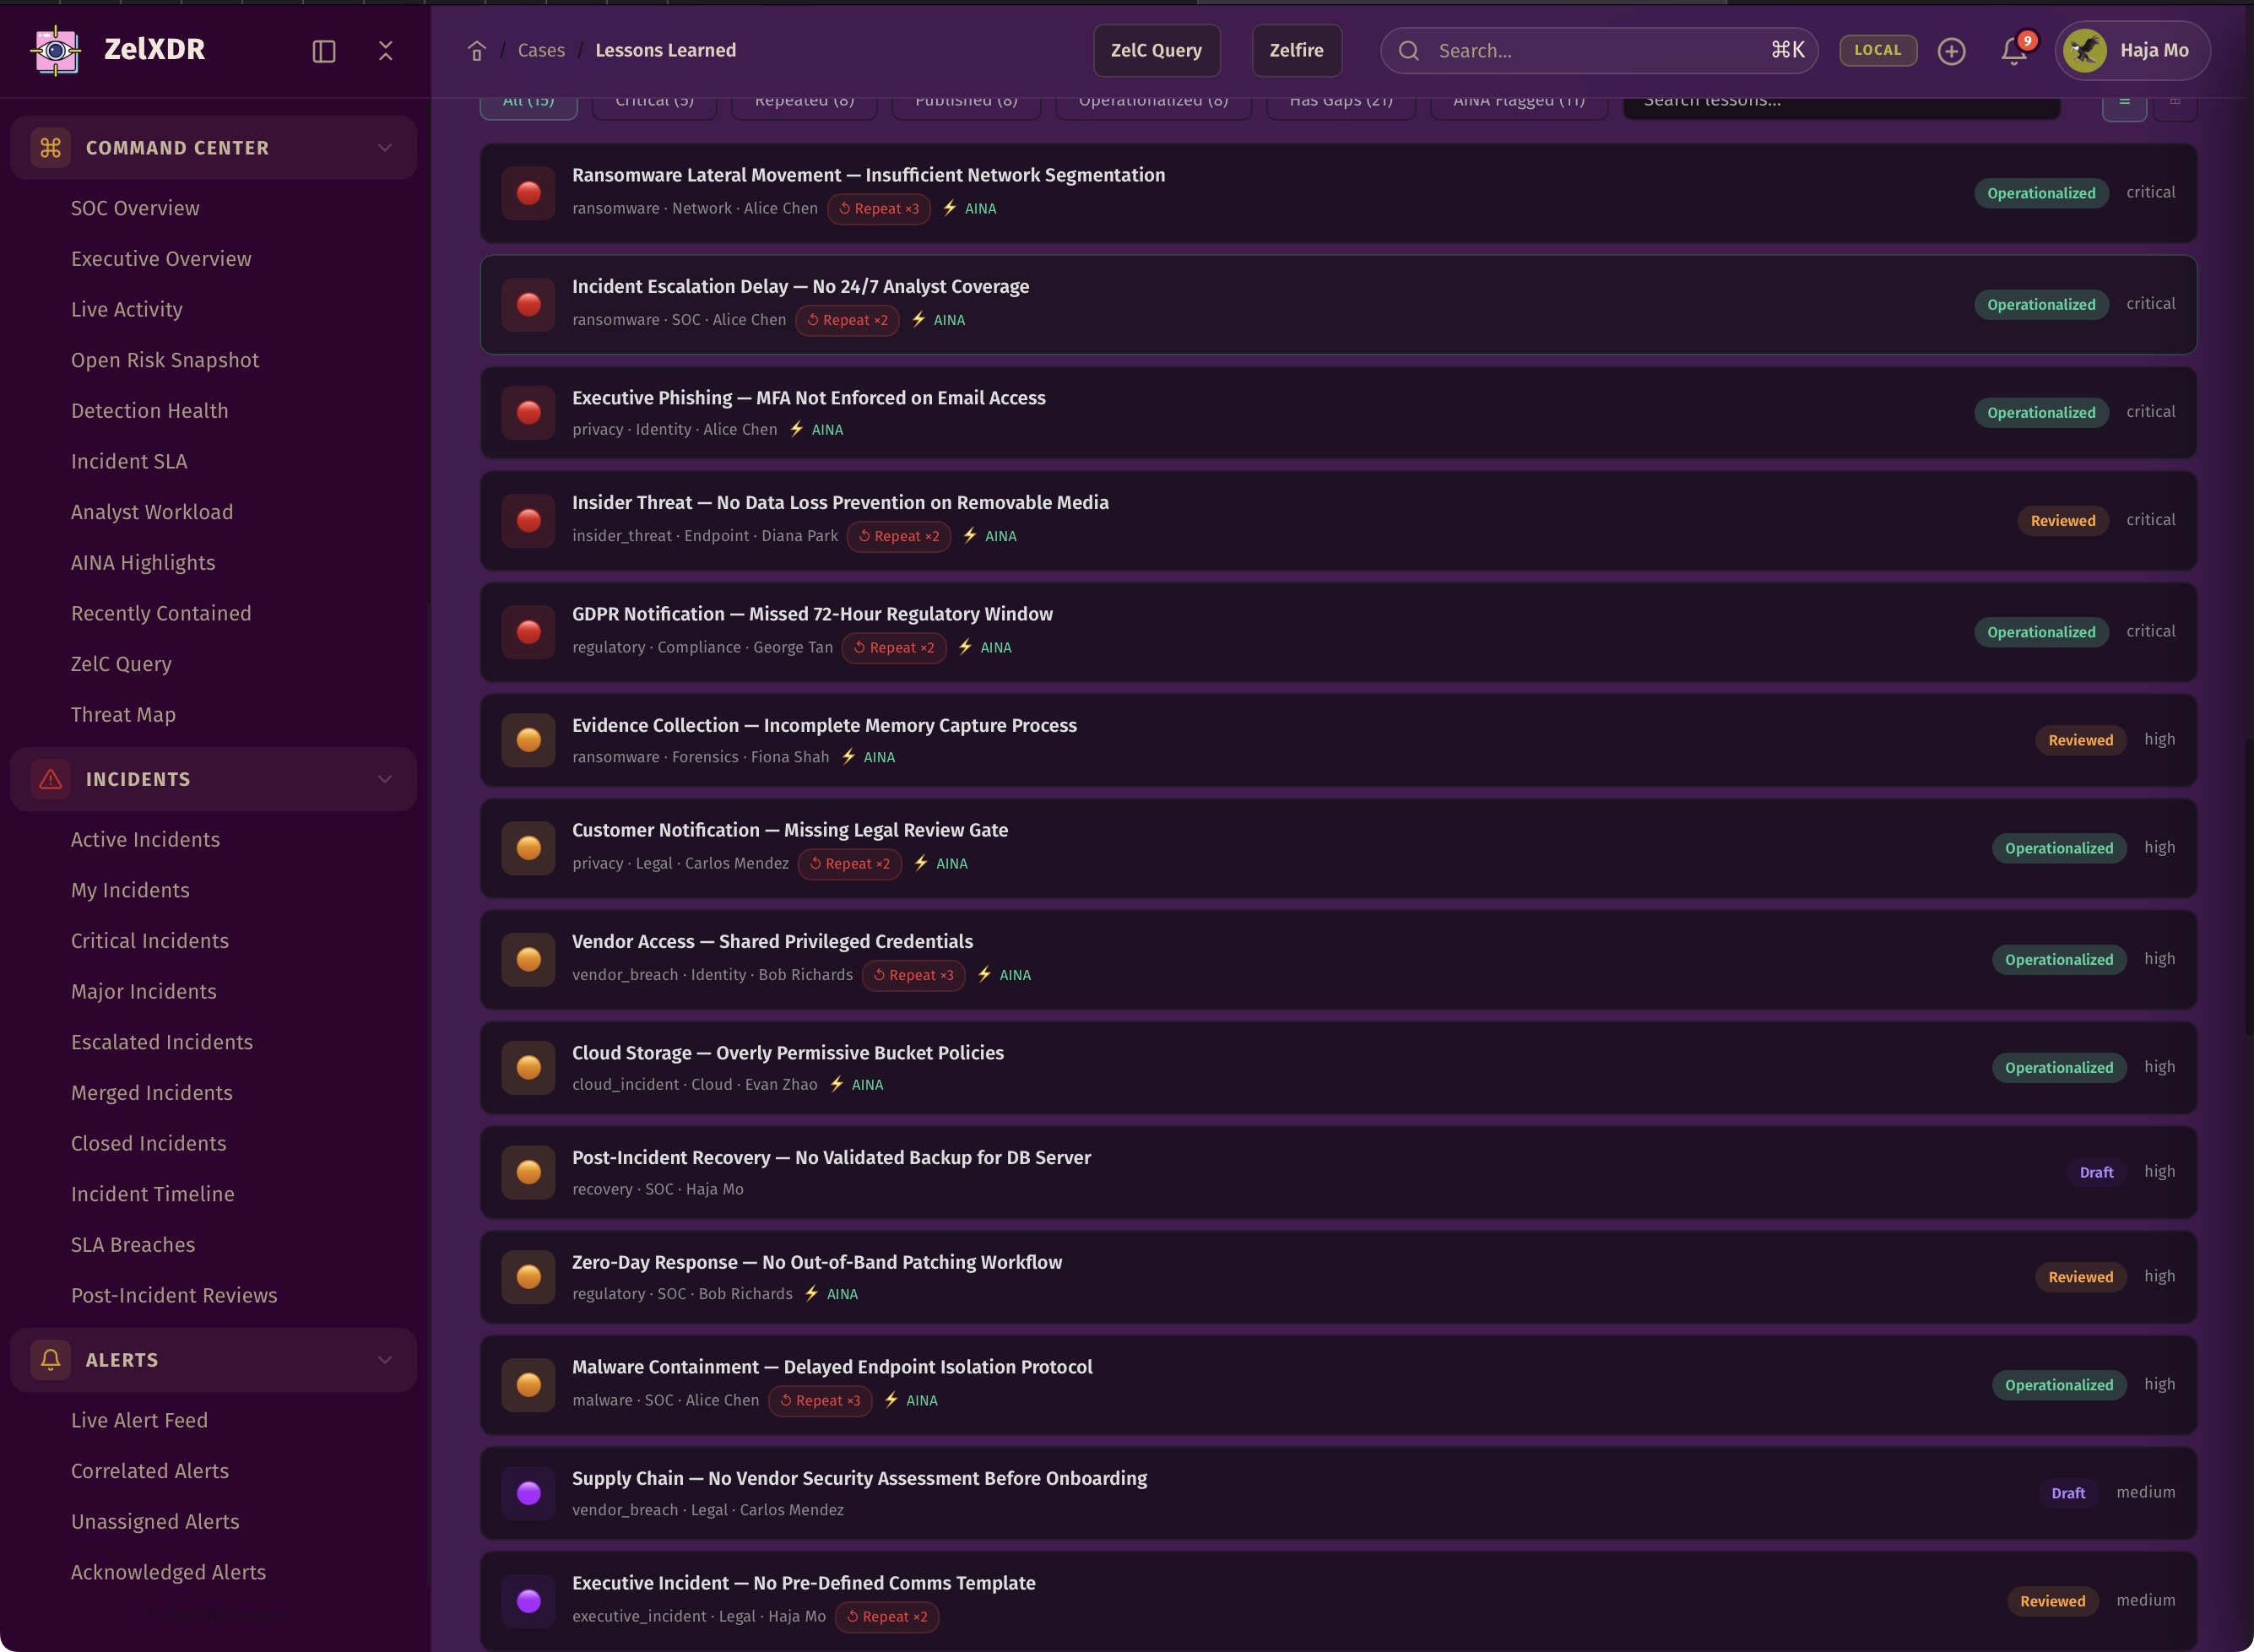
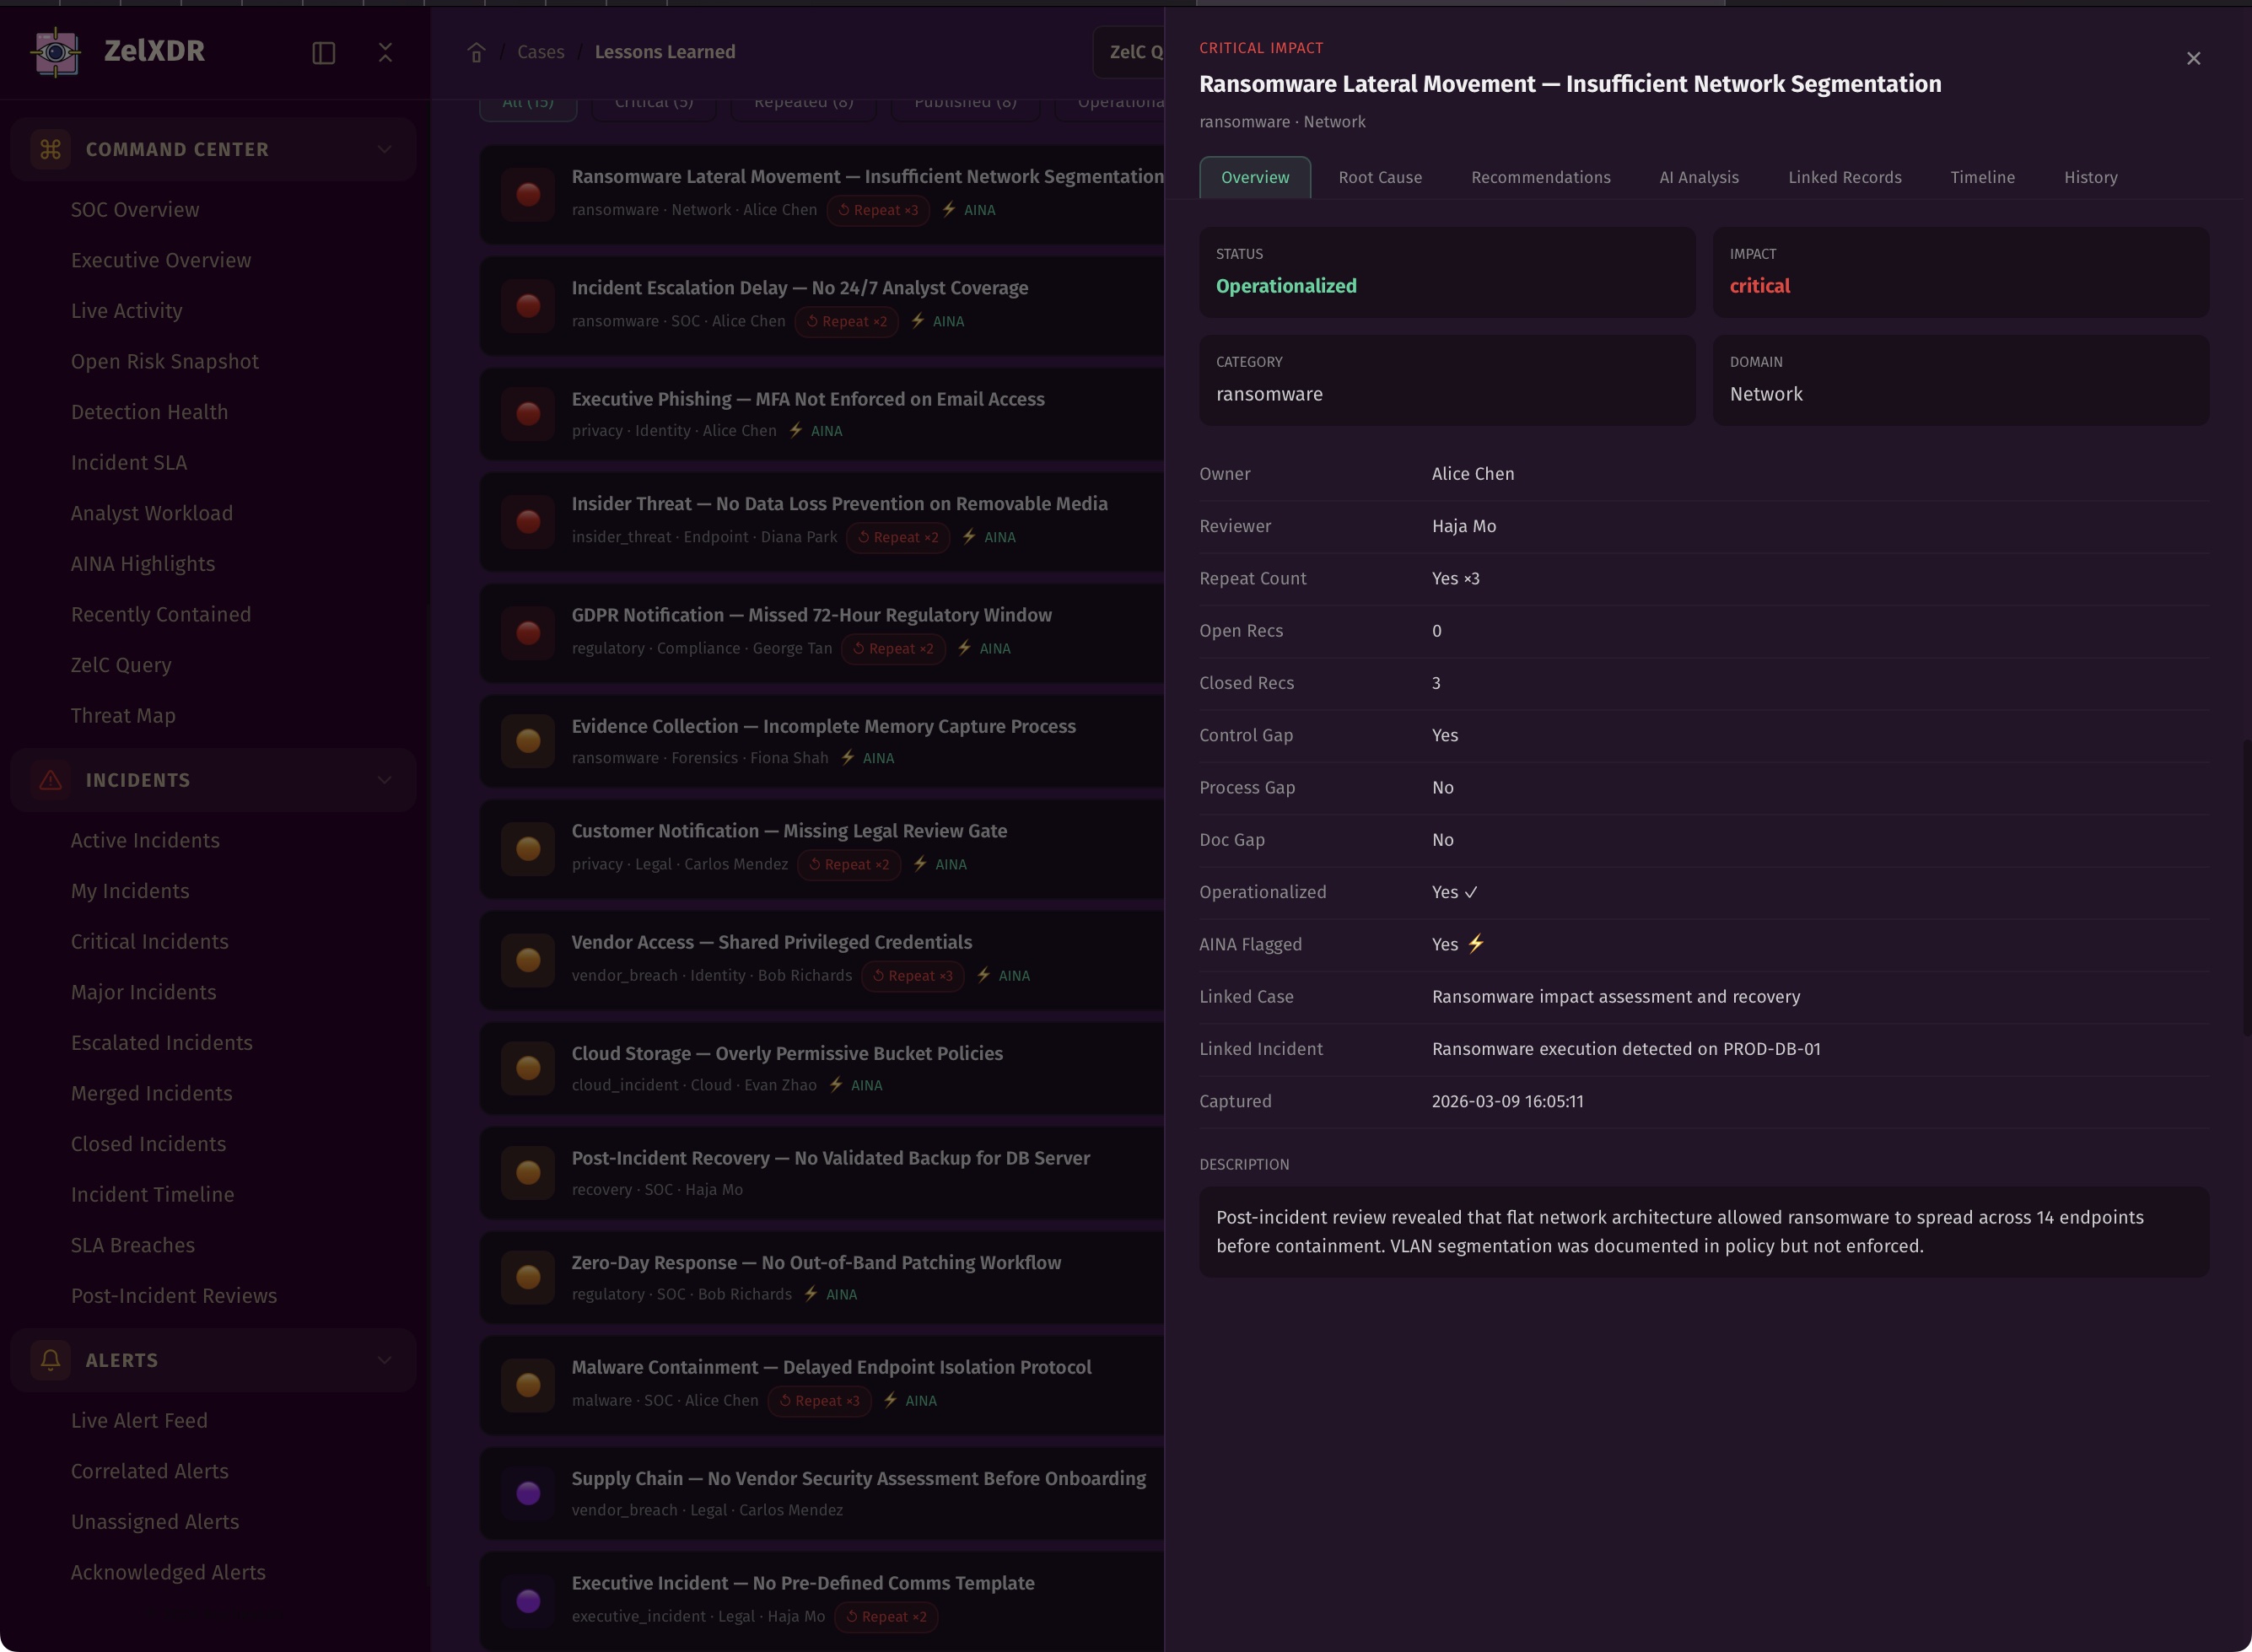
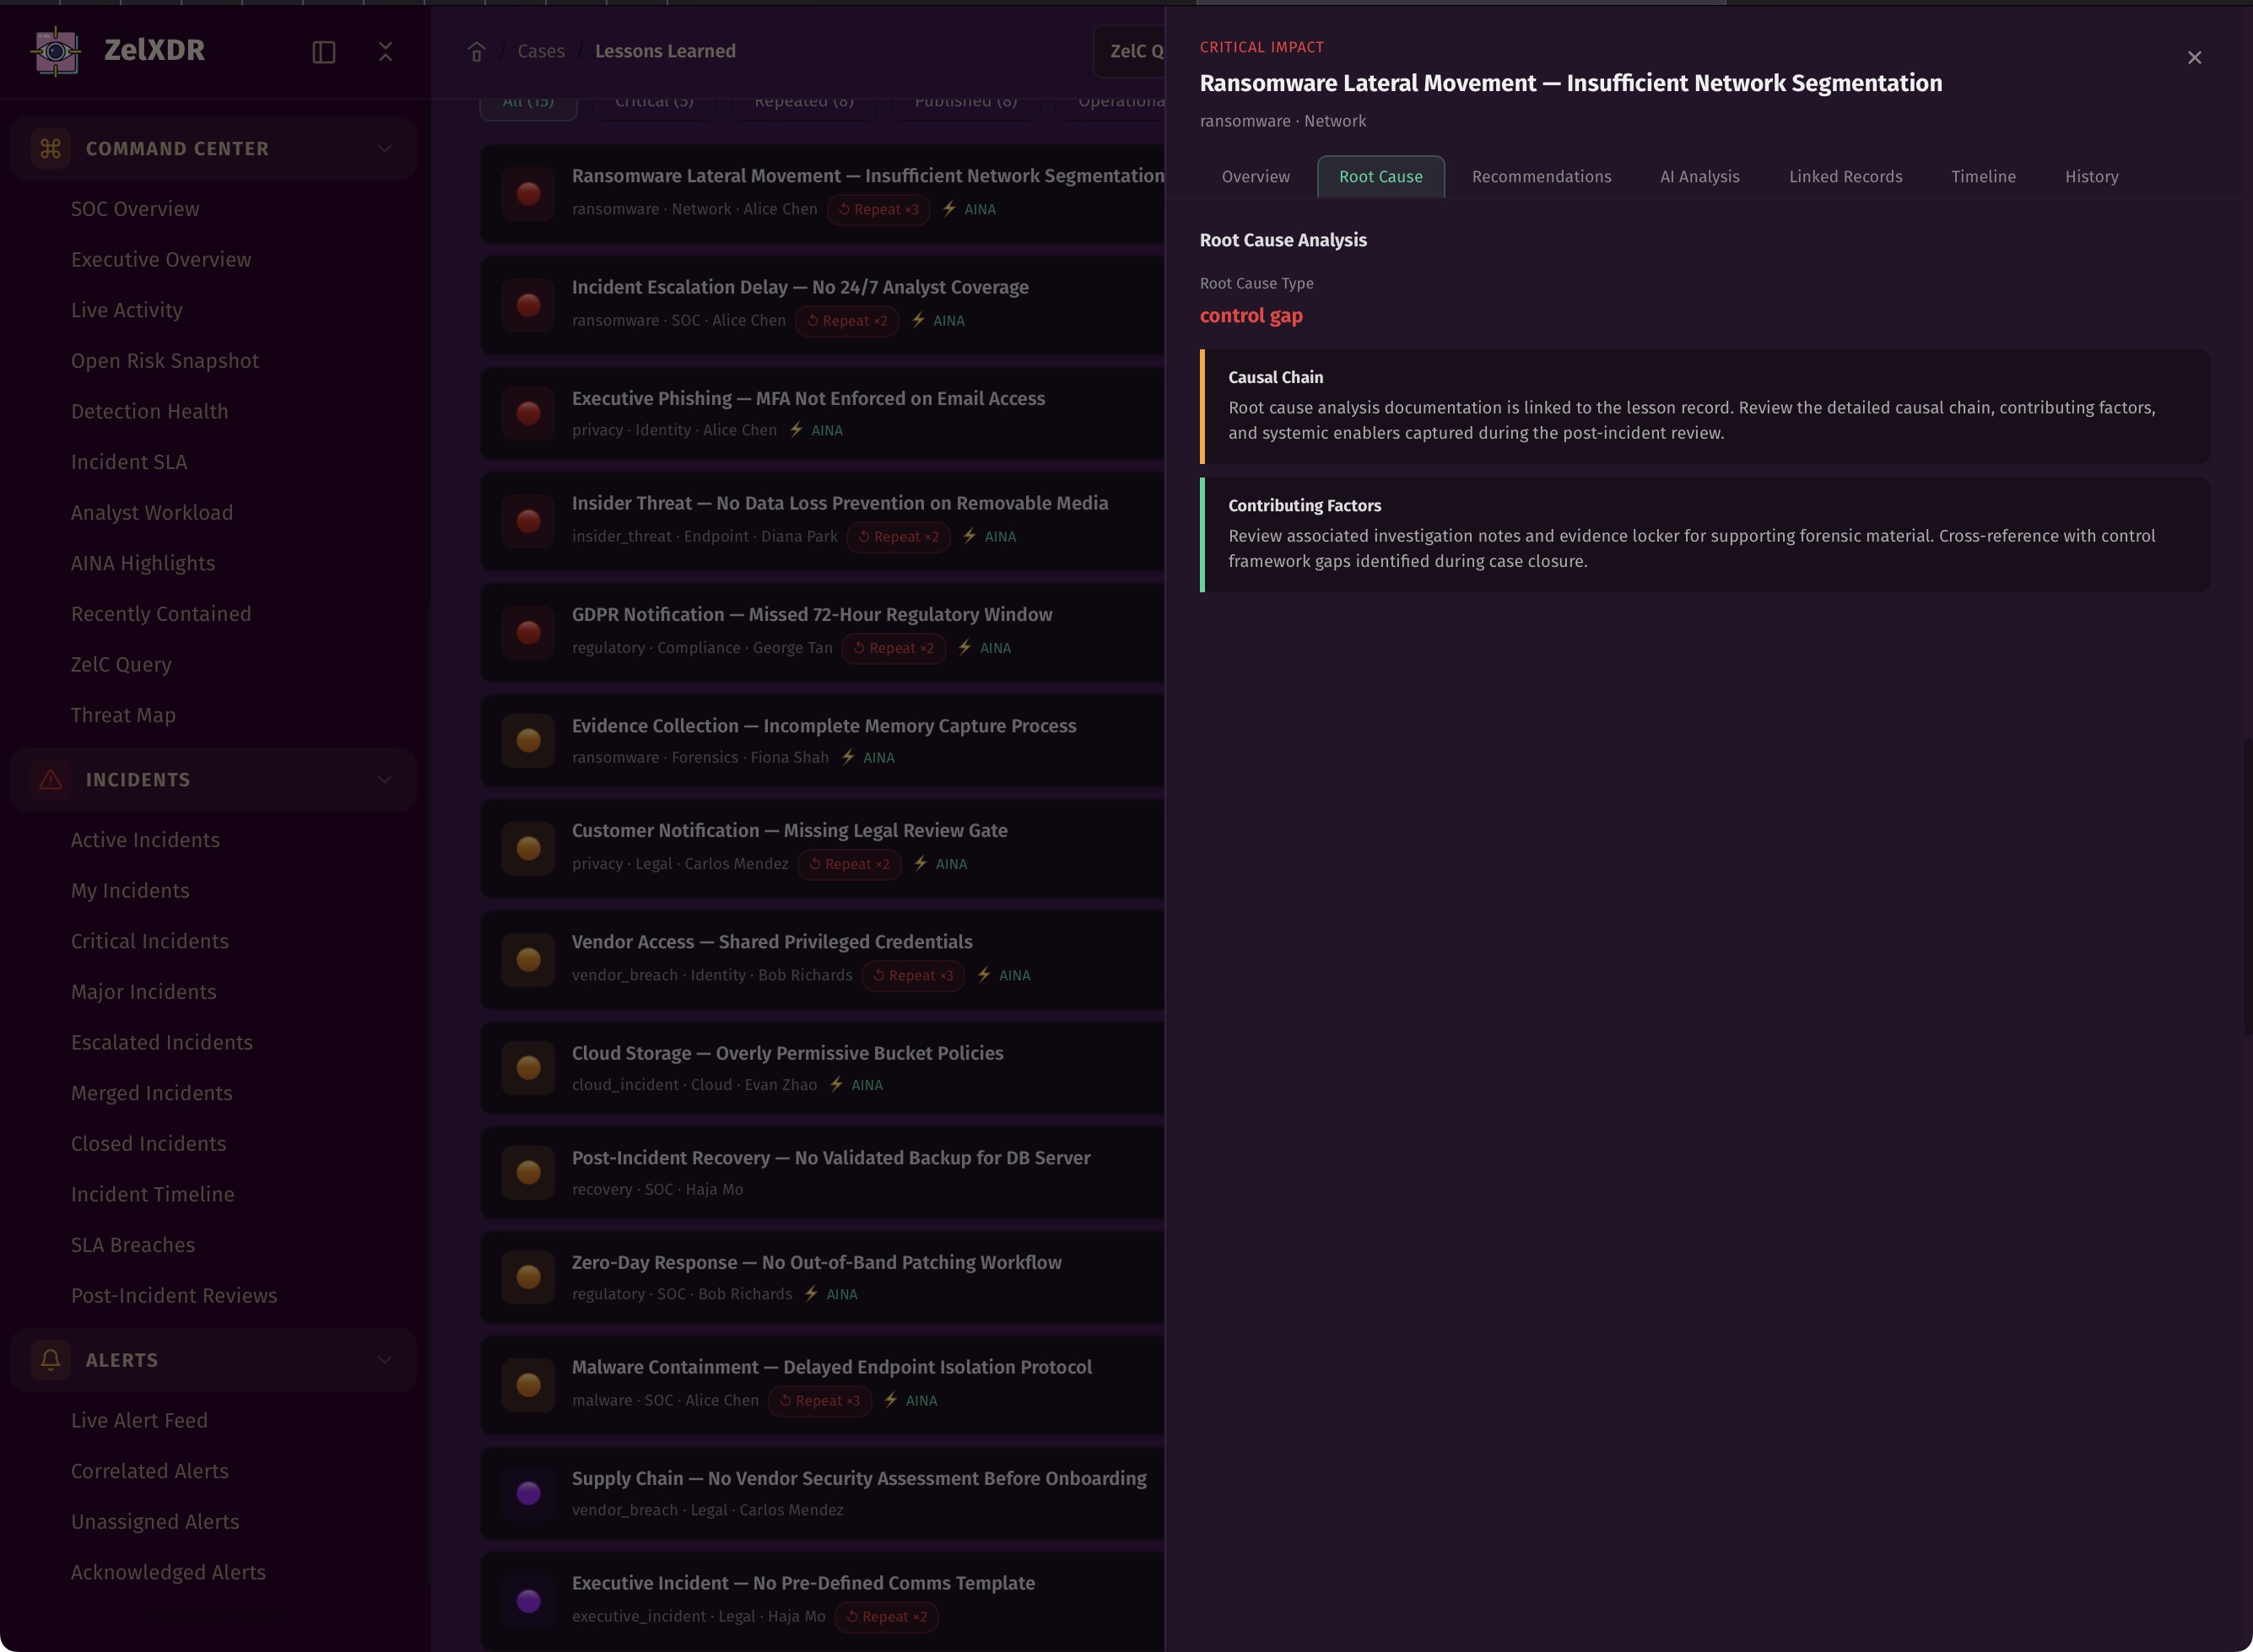
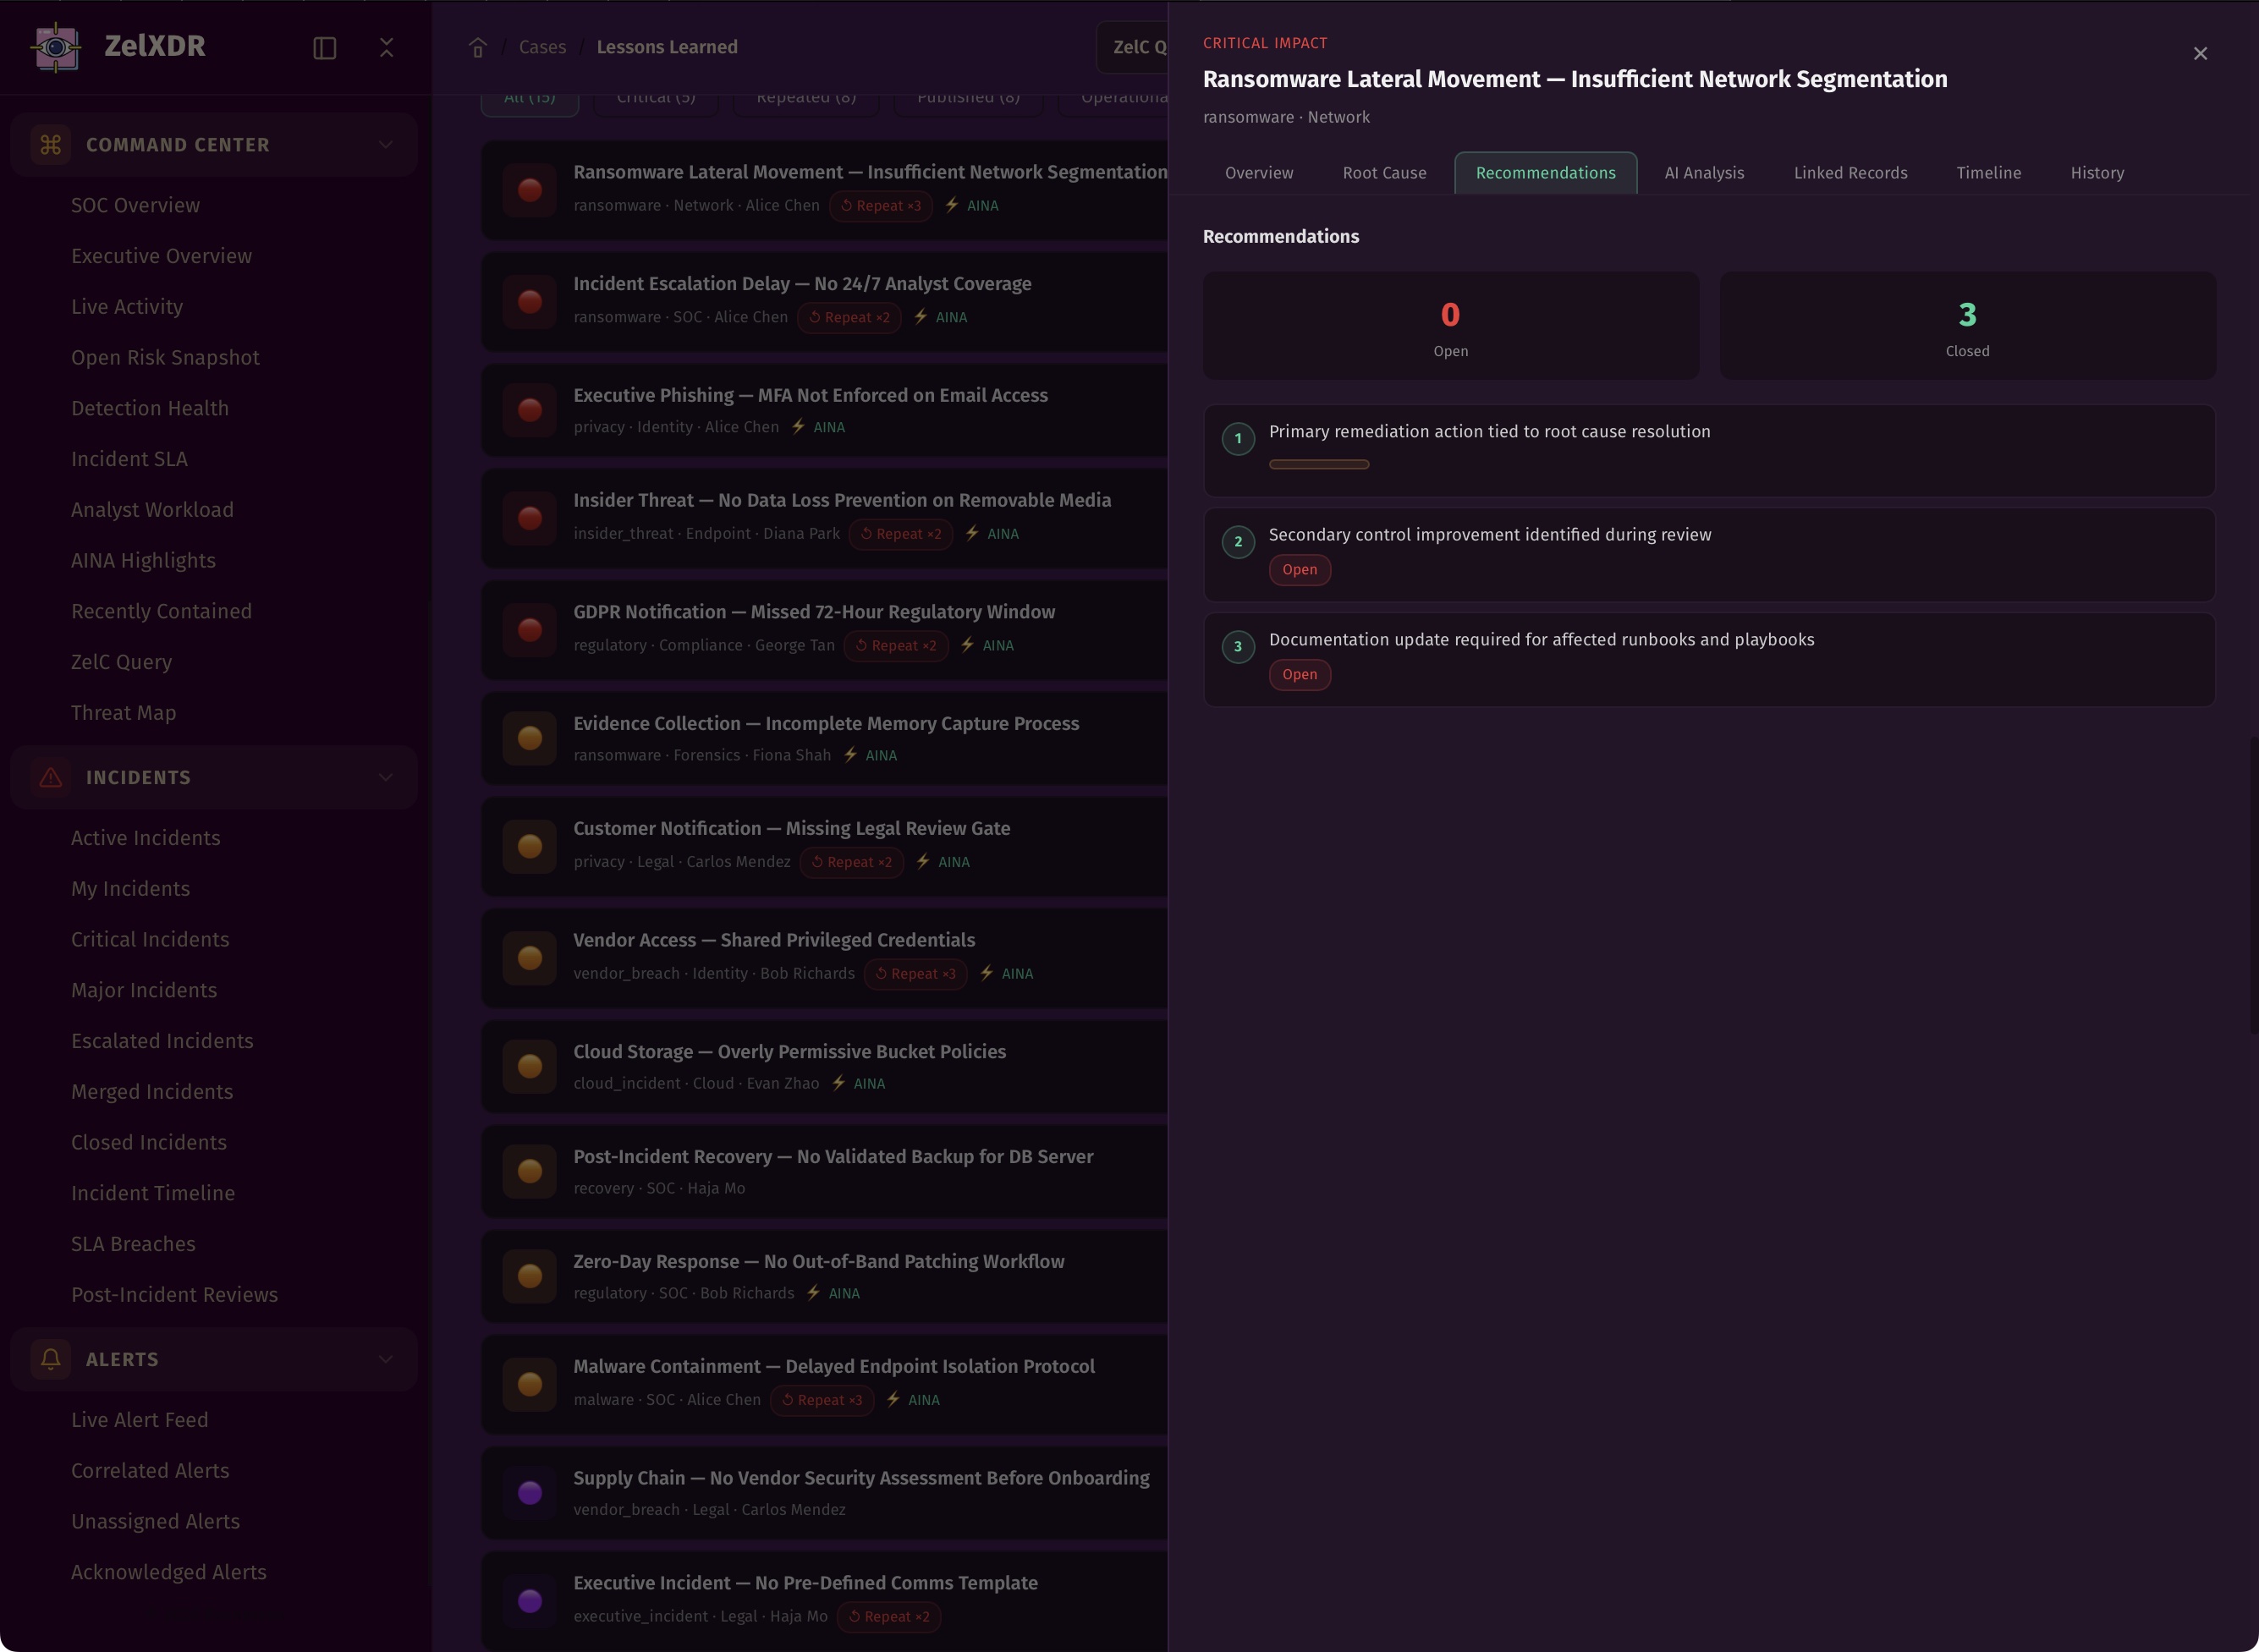
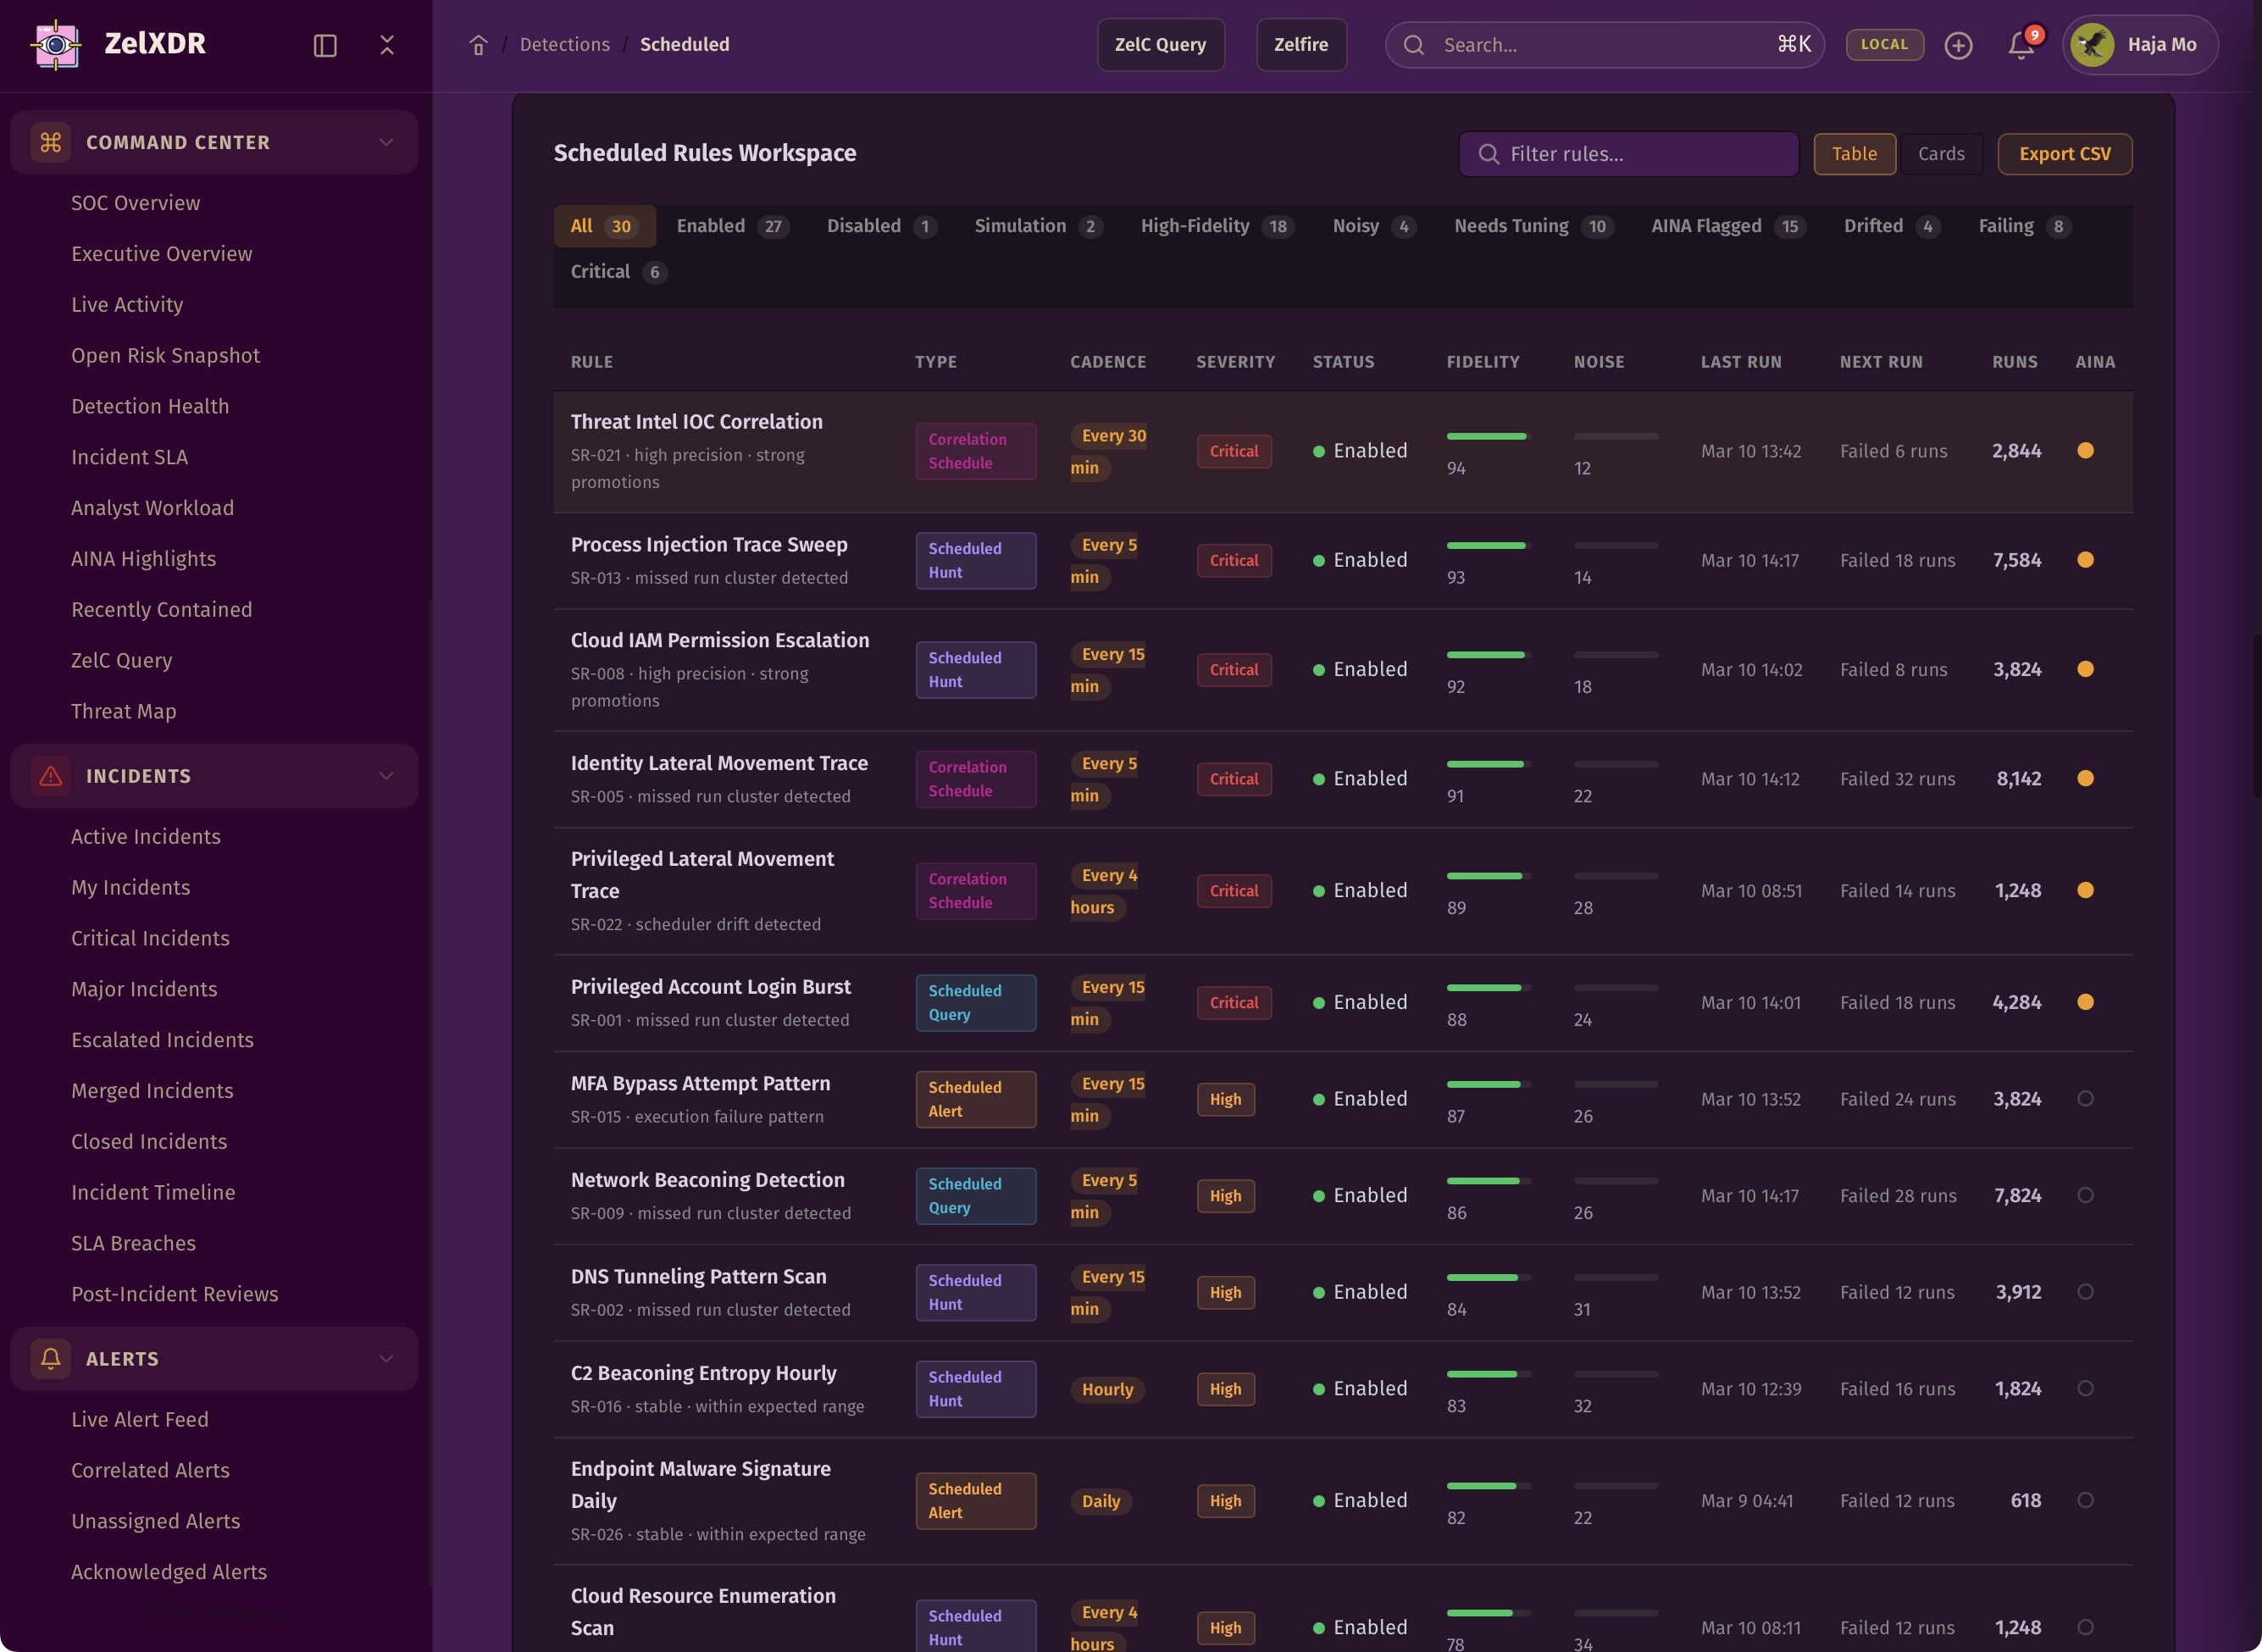
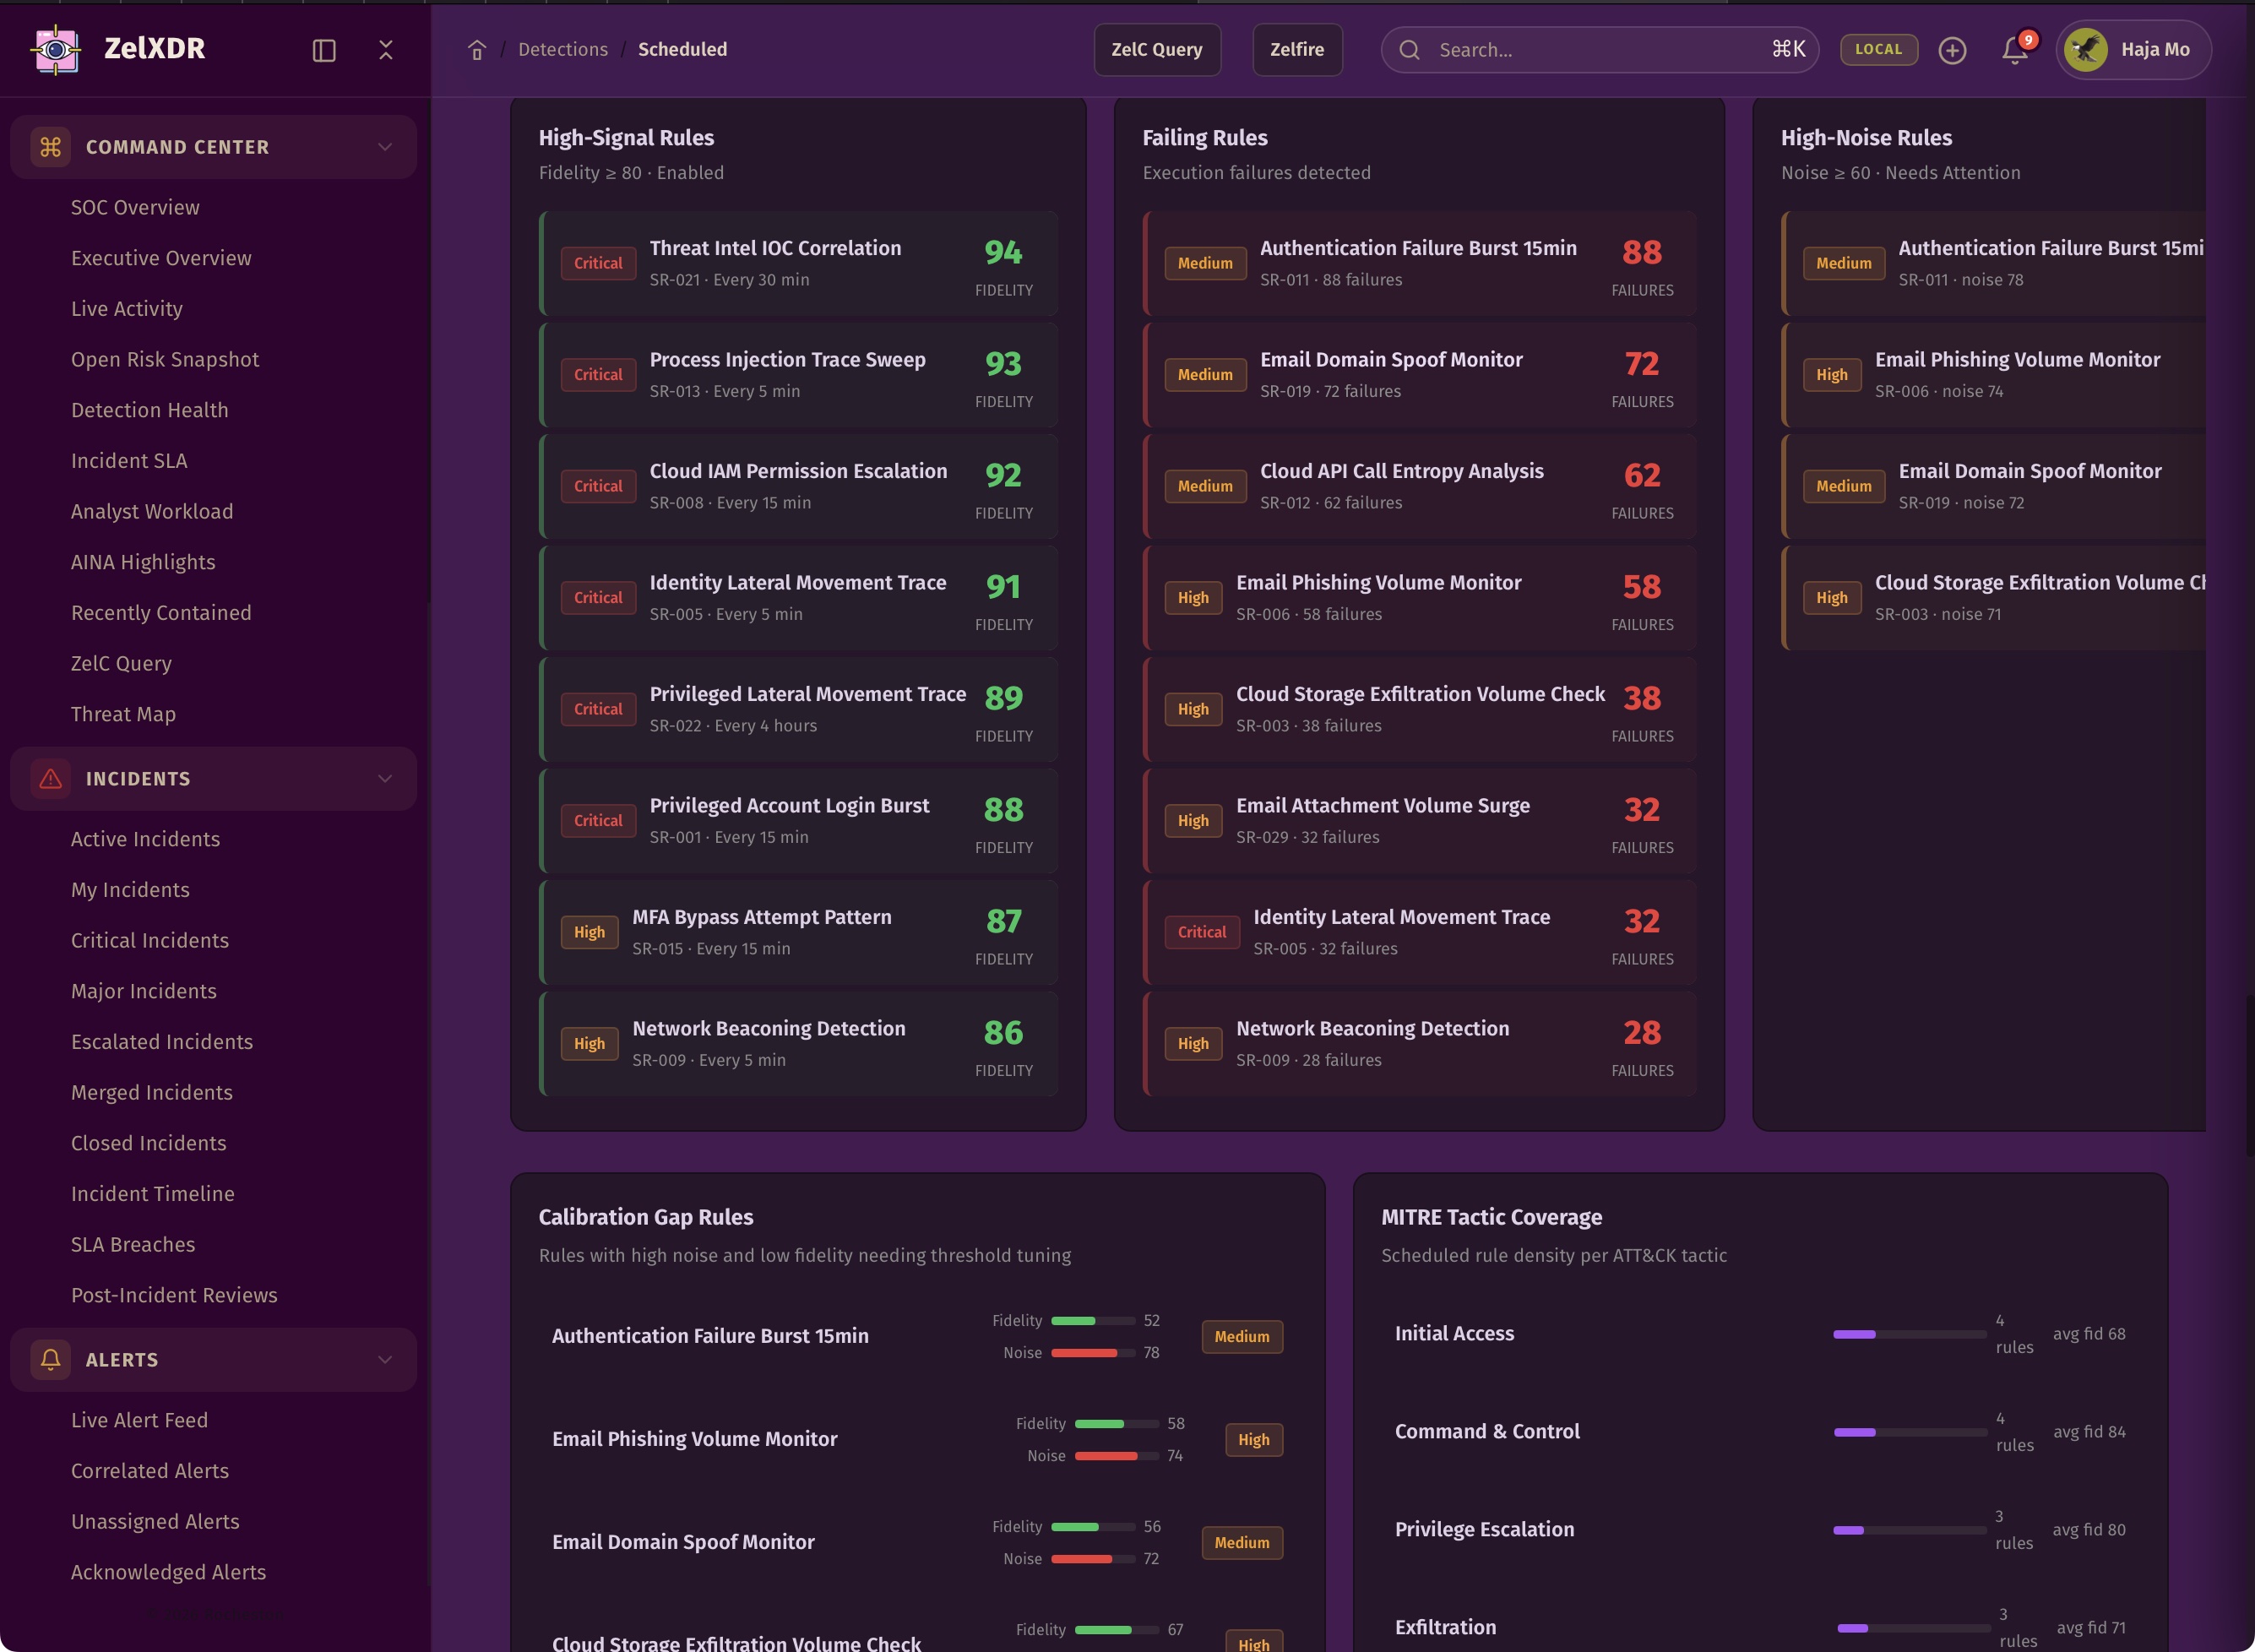
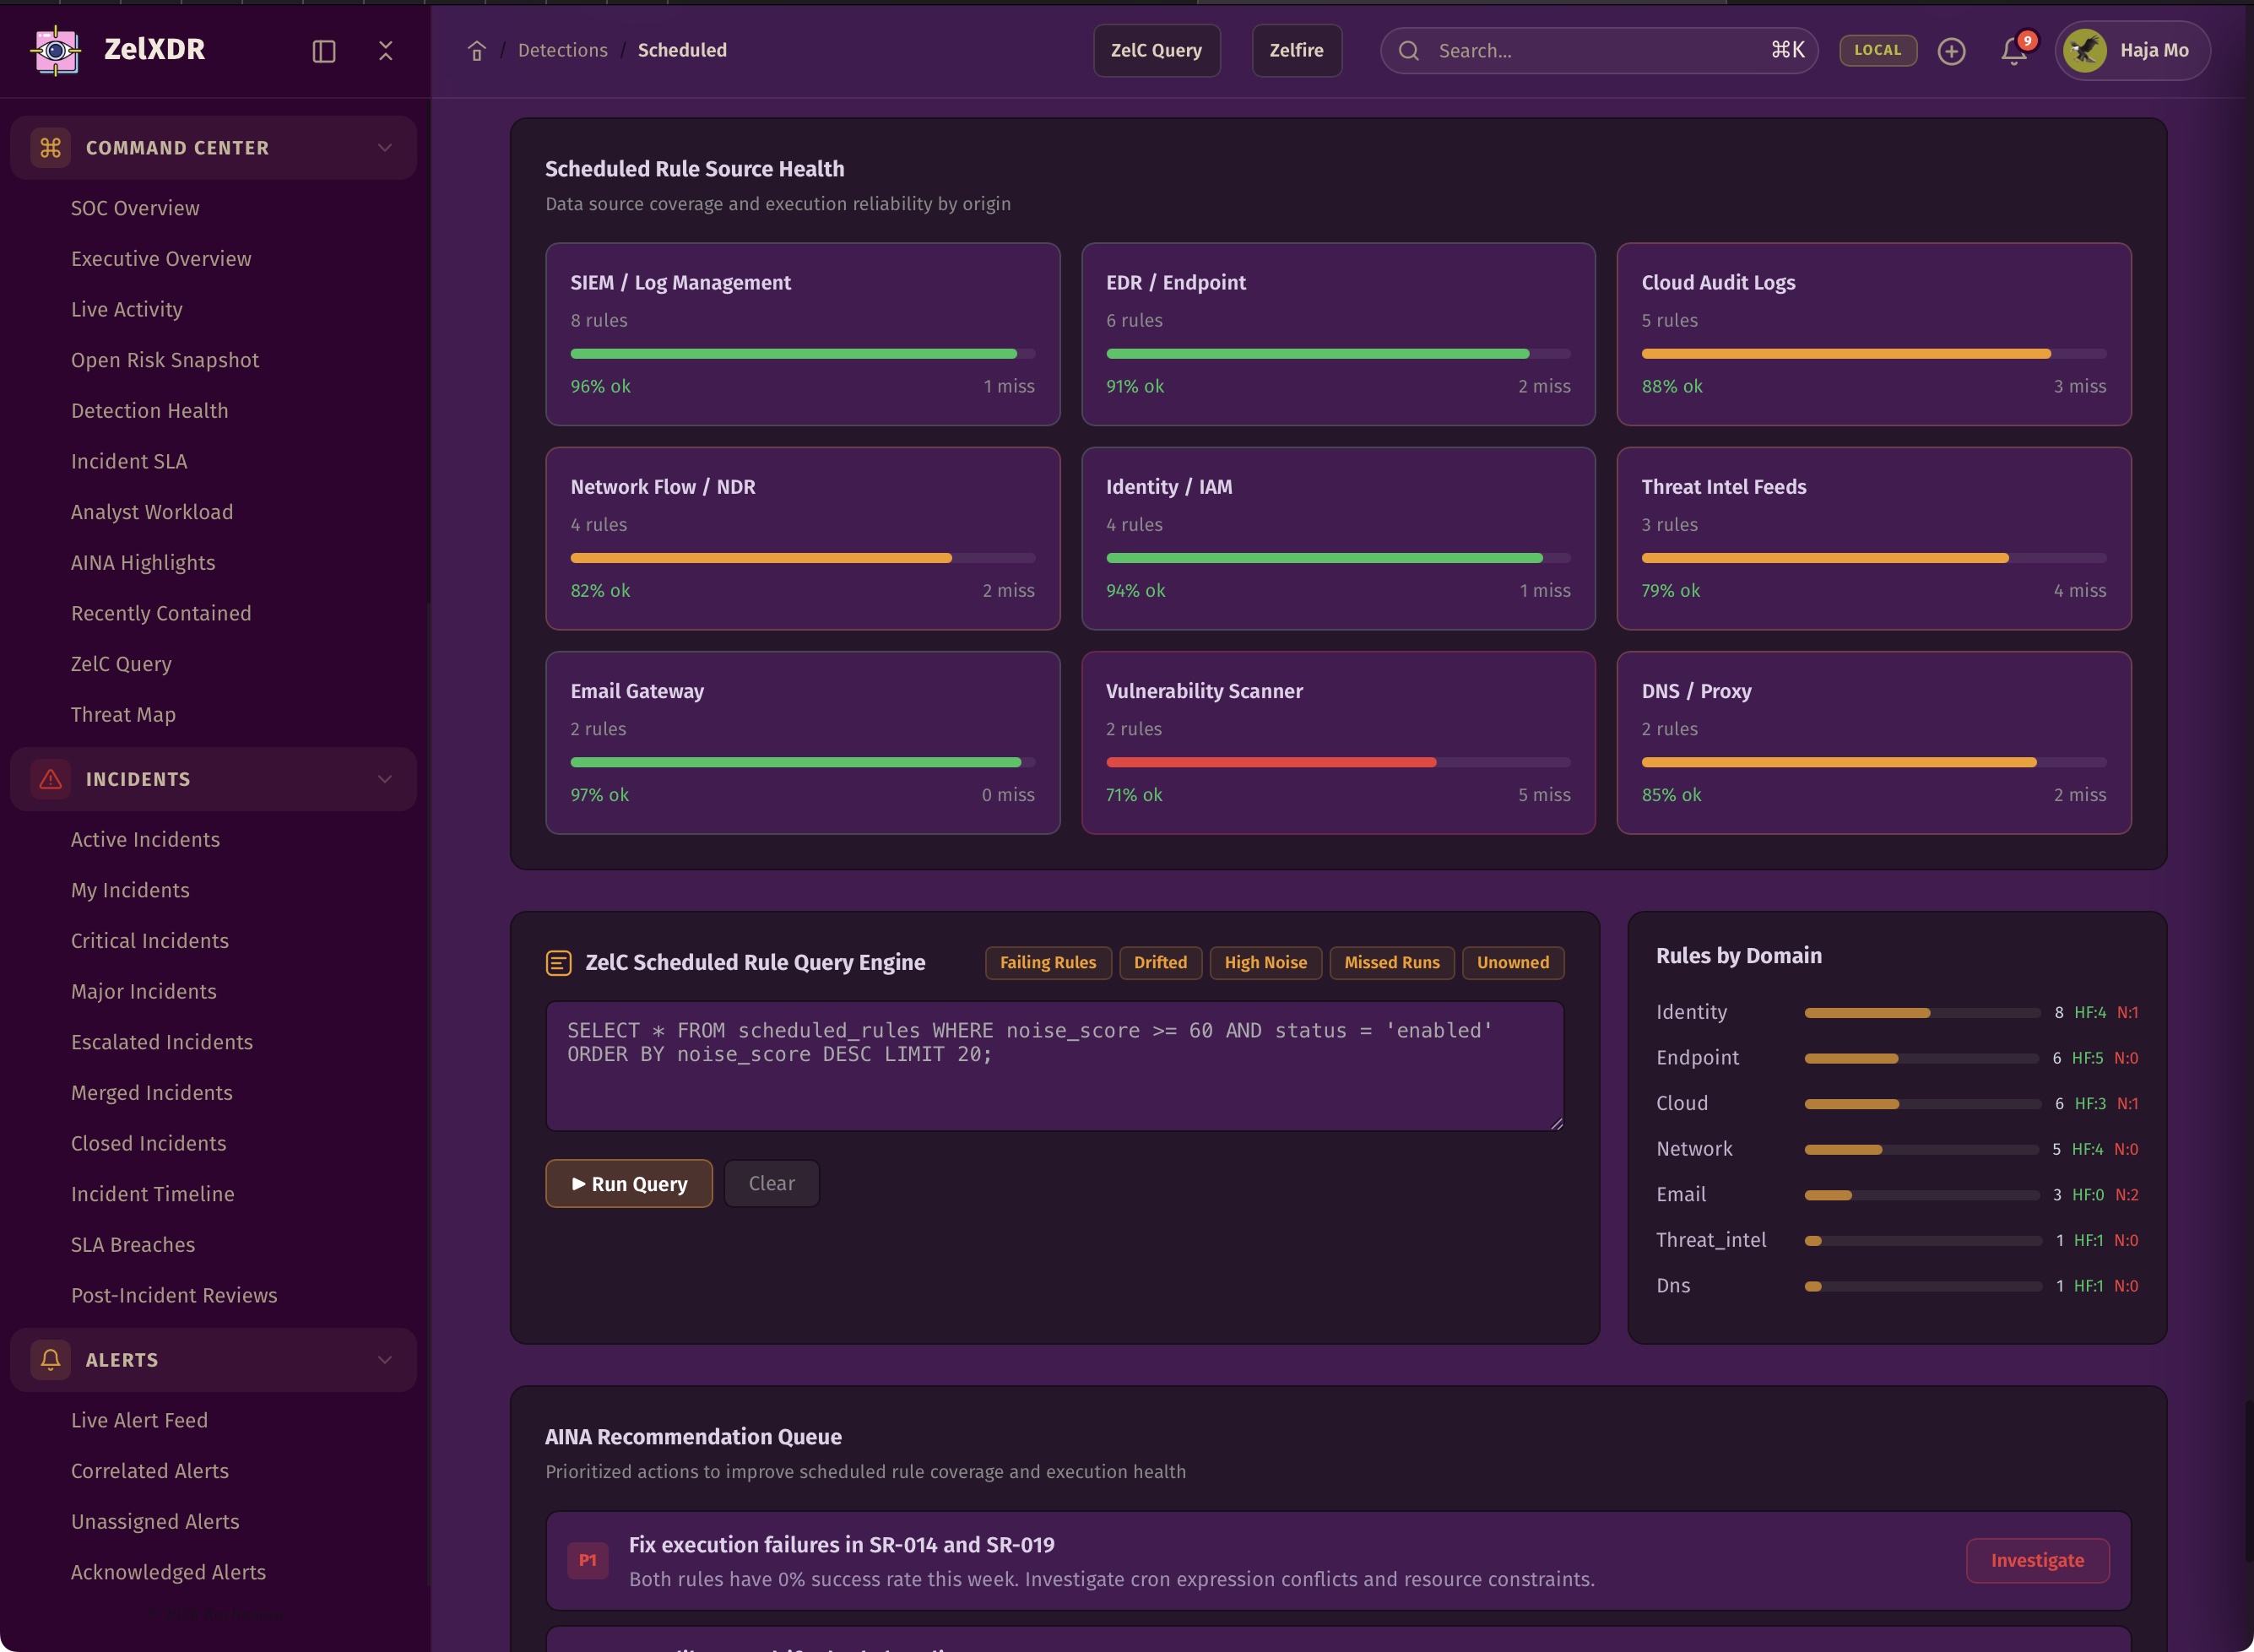
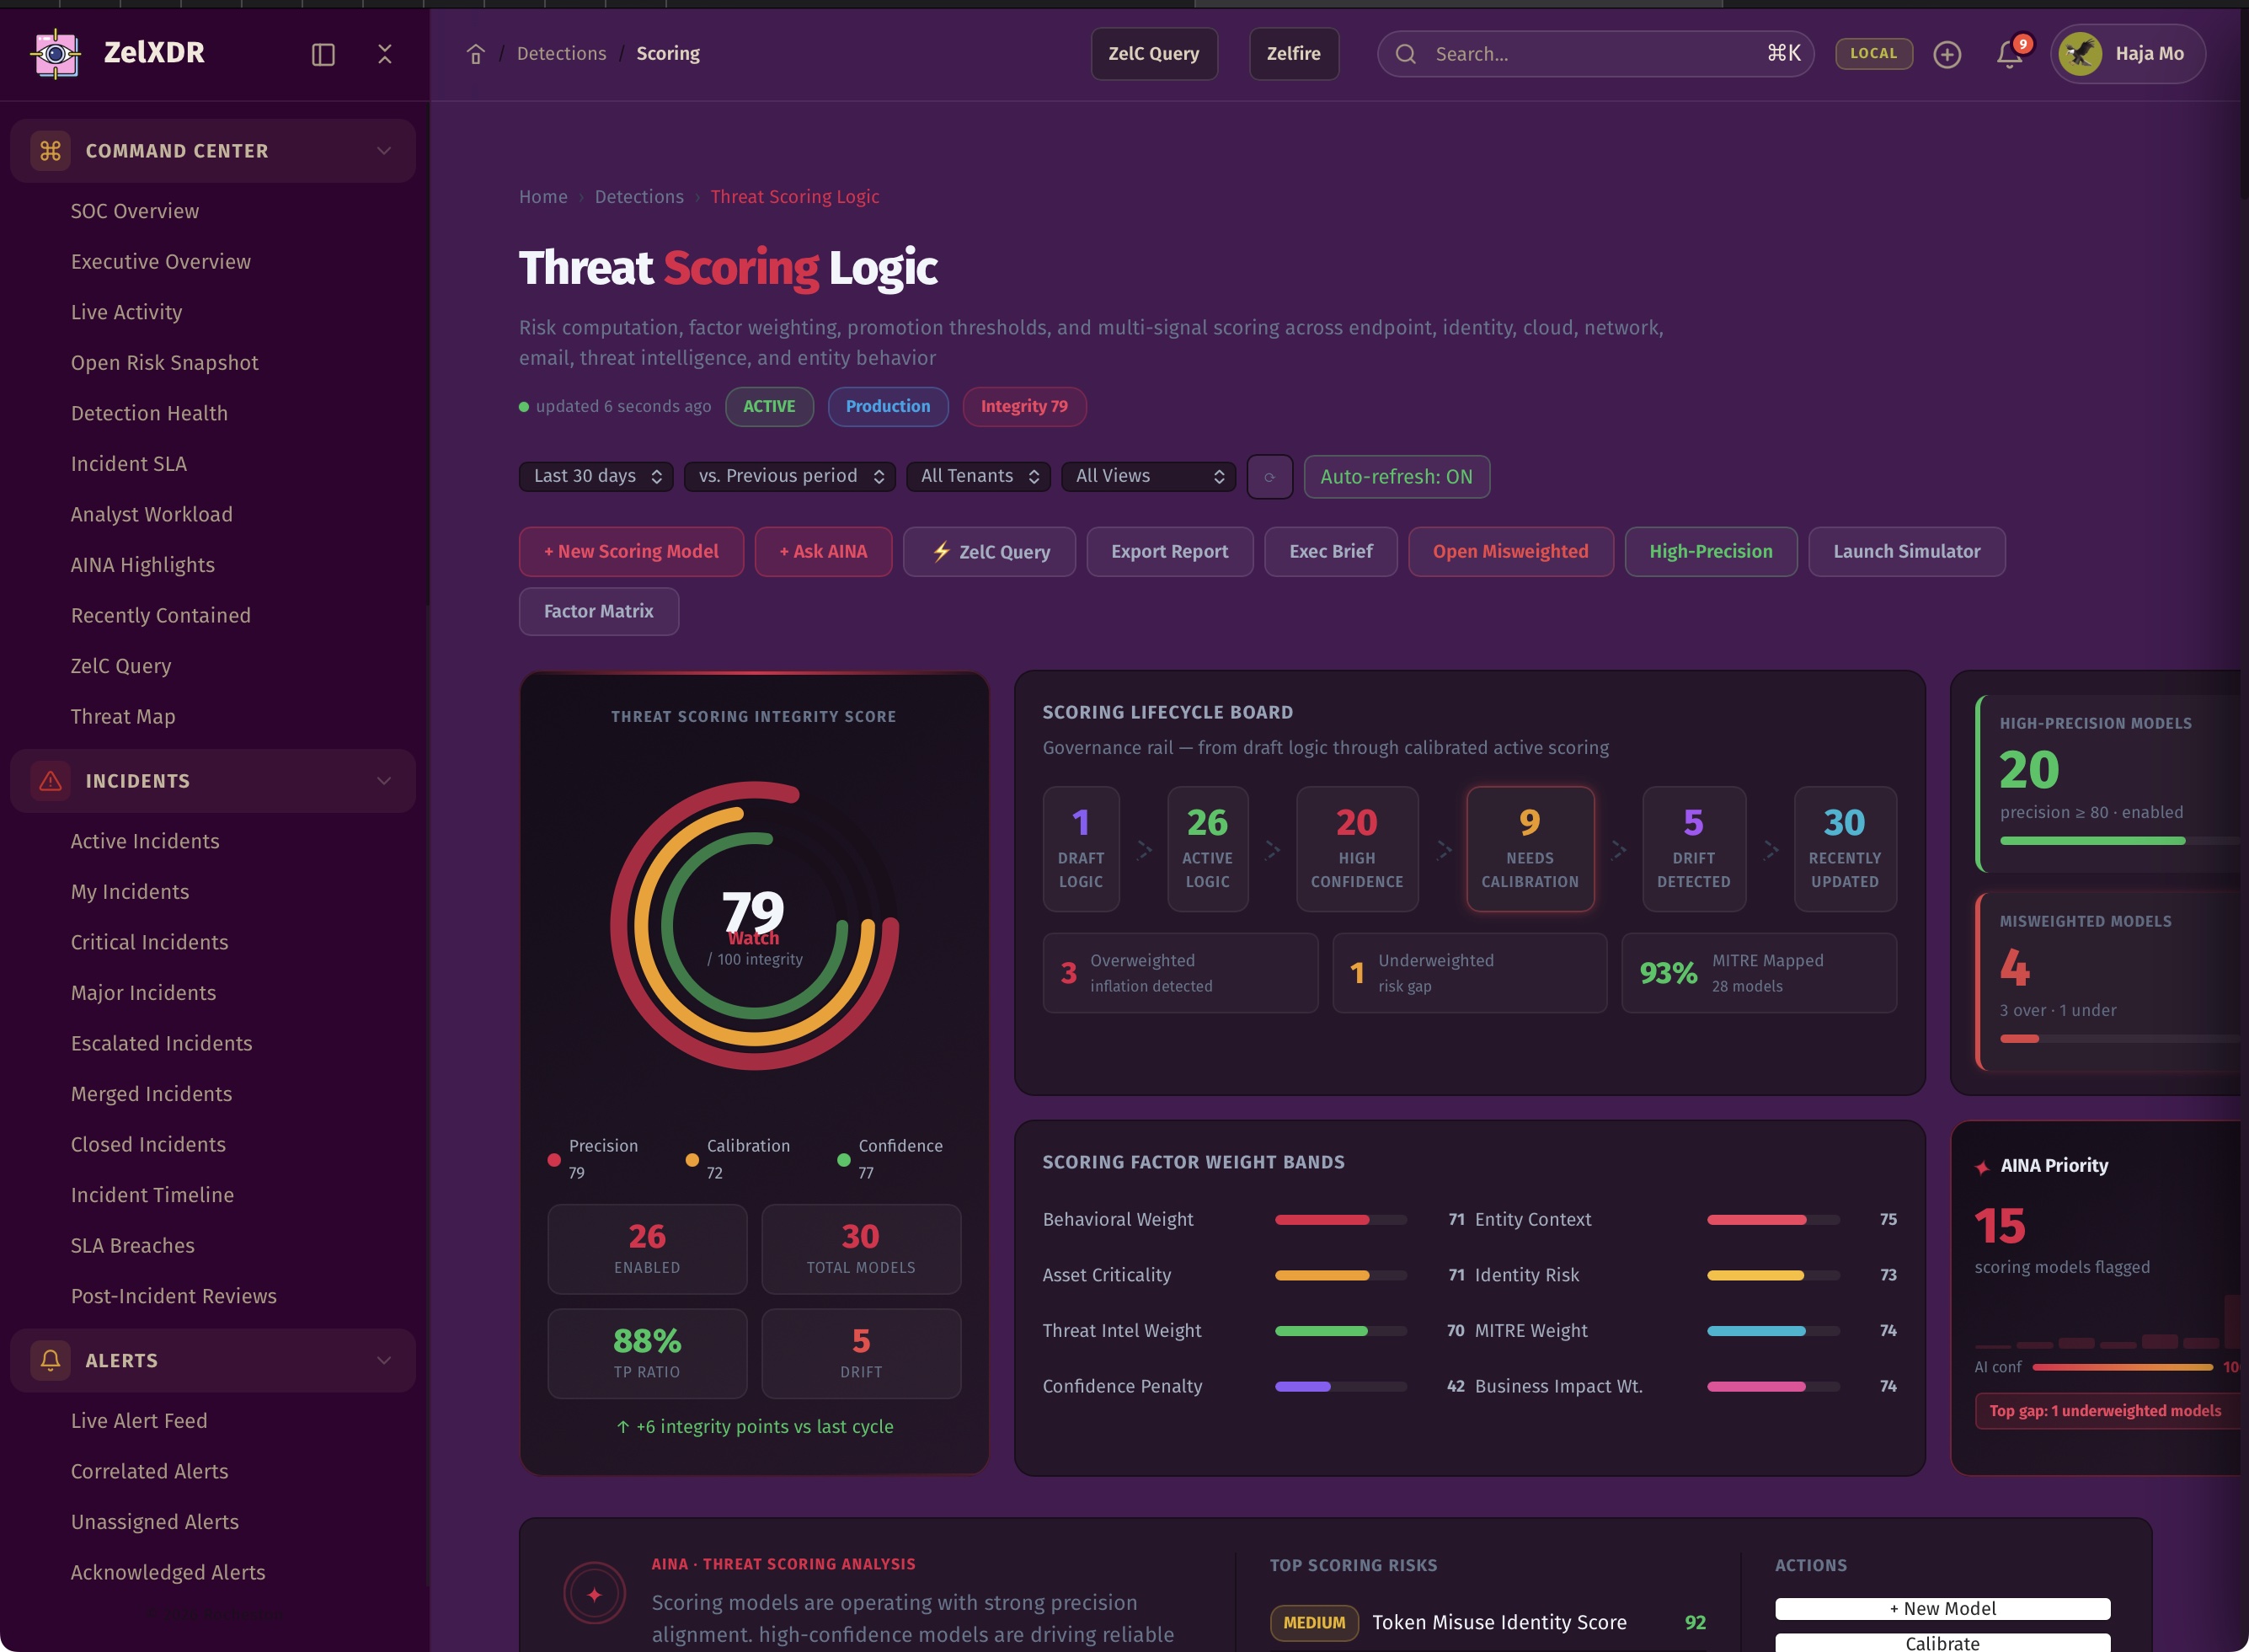
Explore 354 product screenshots. Select any image for a closer look.
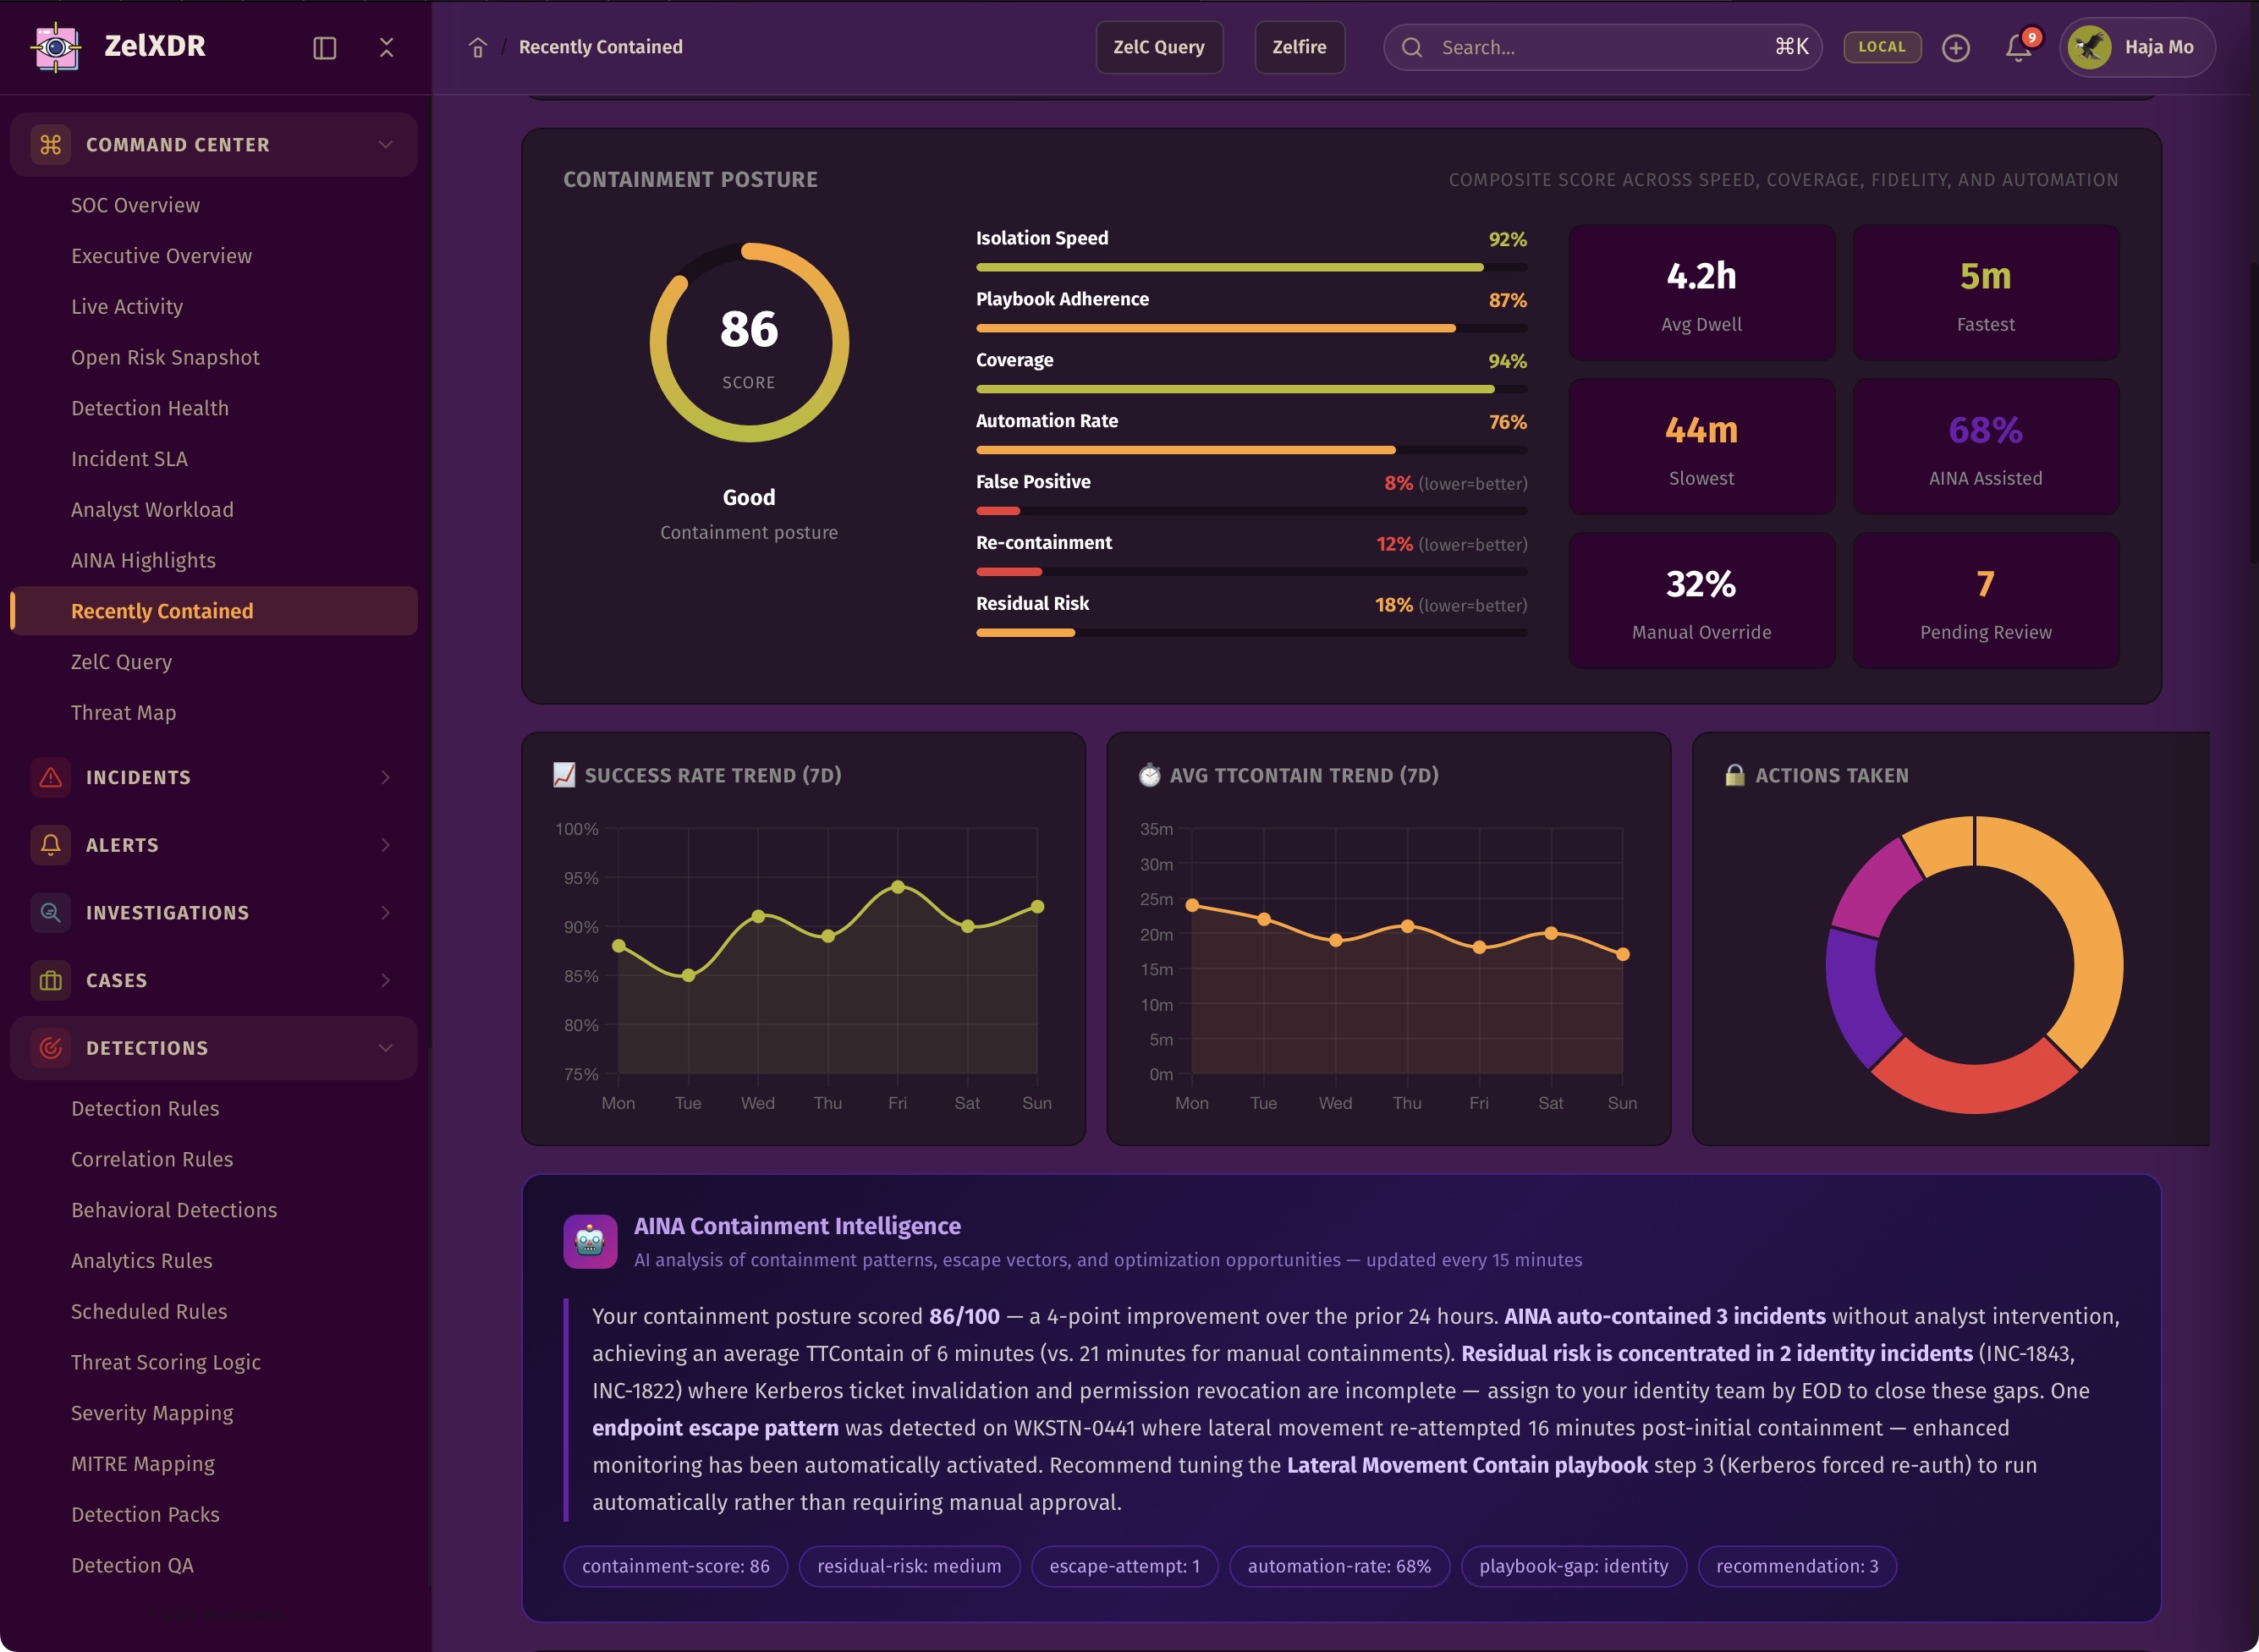
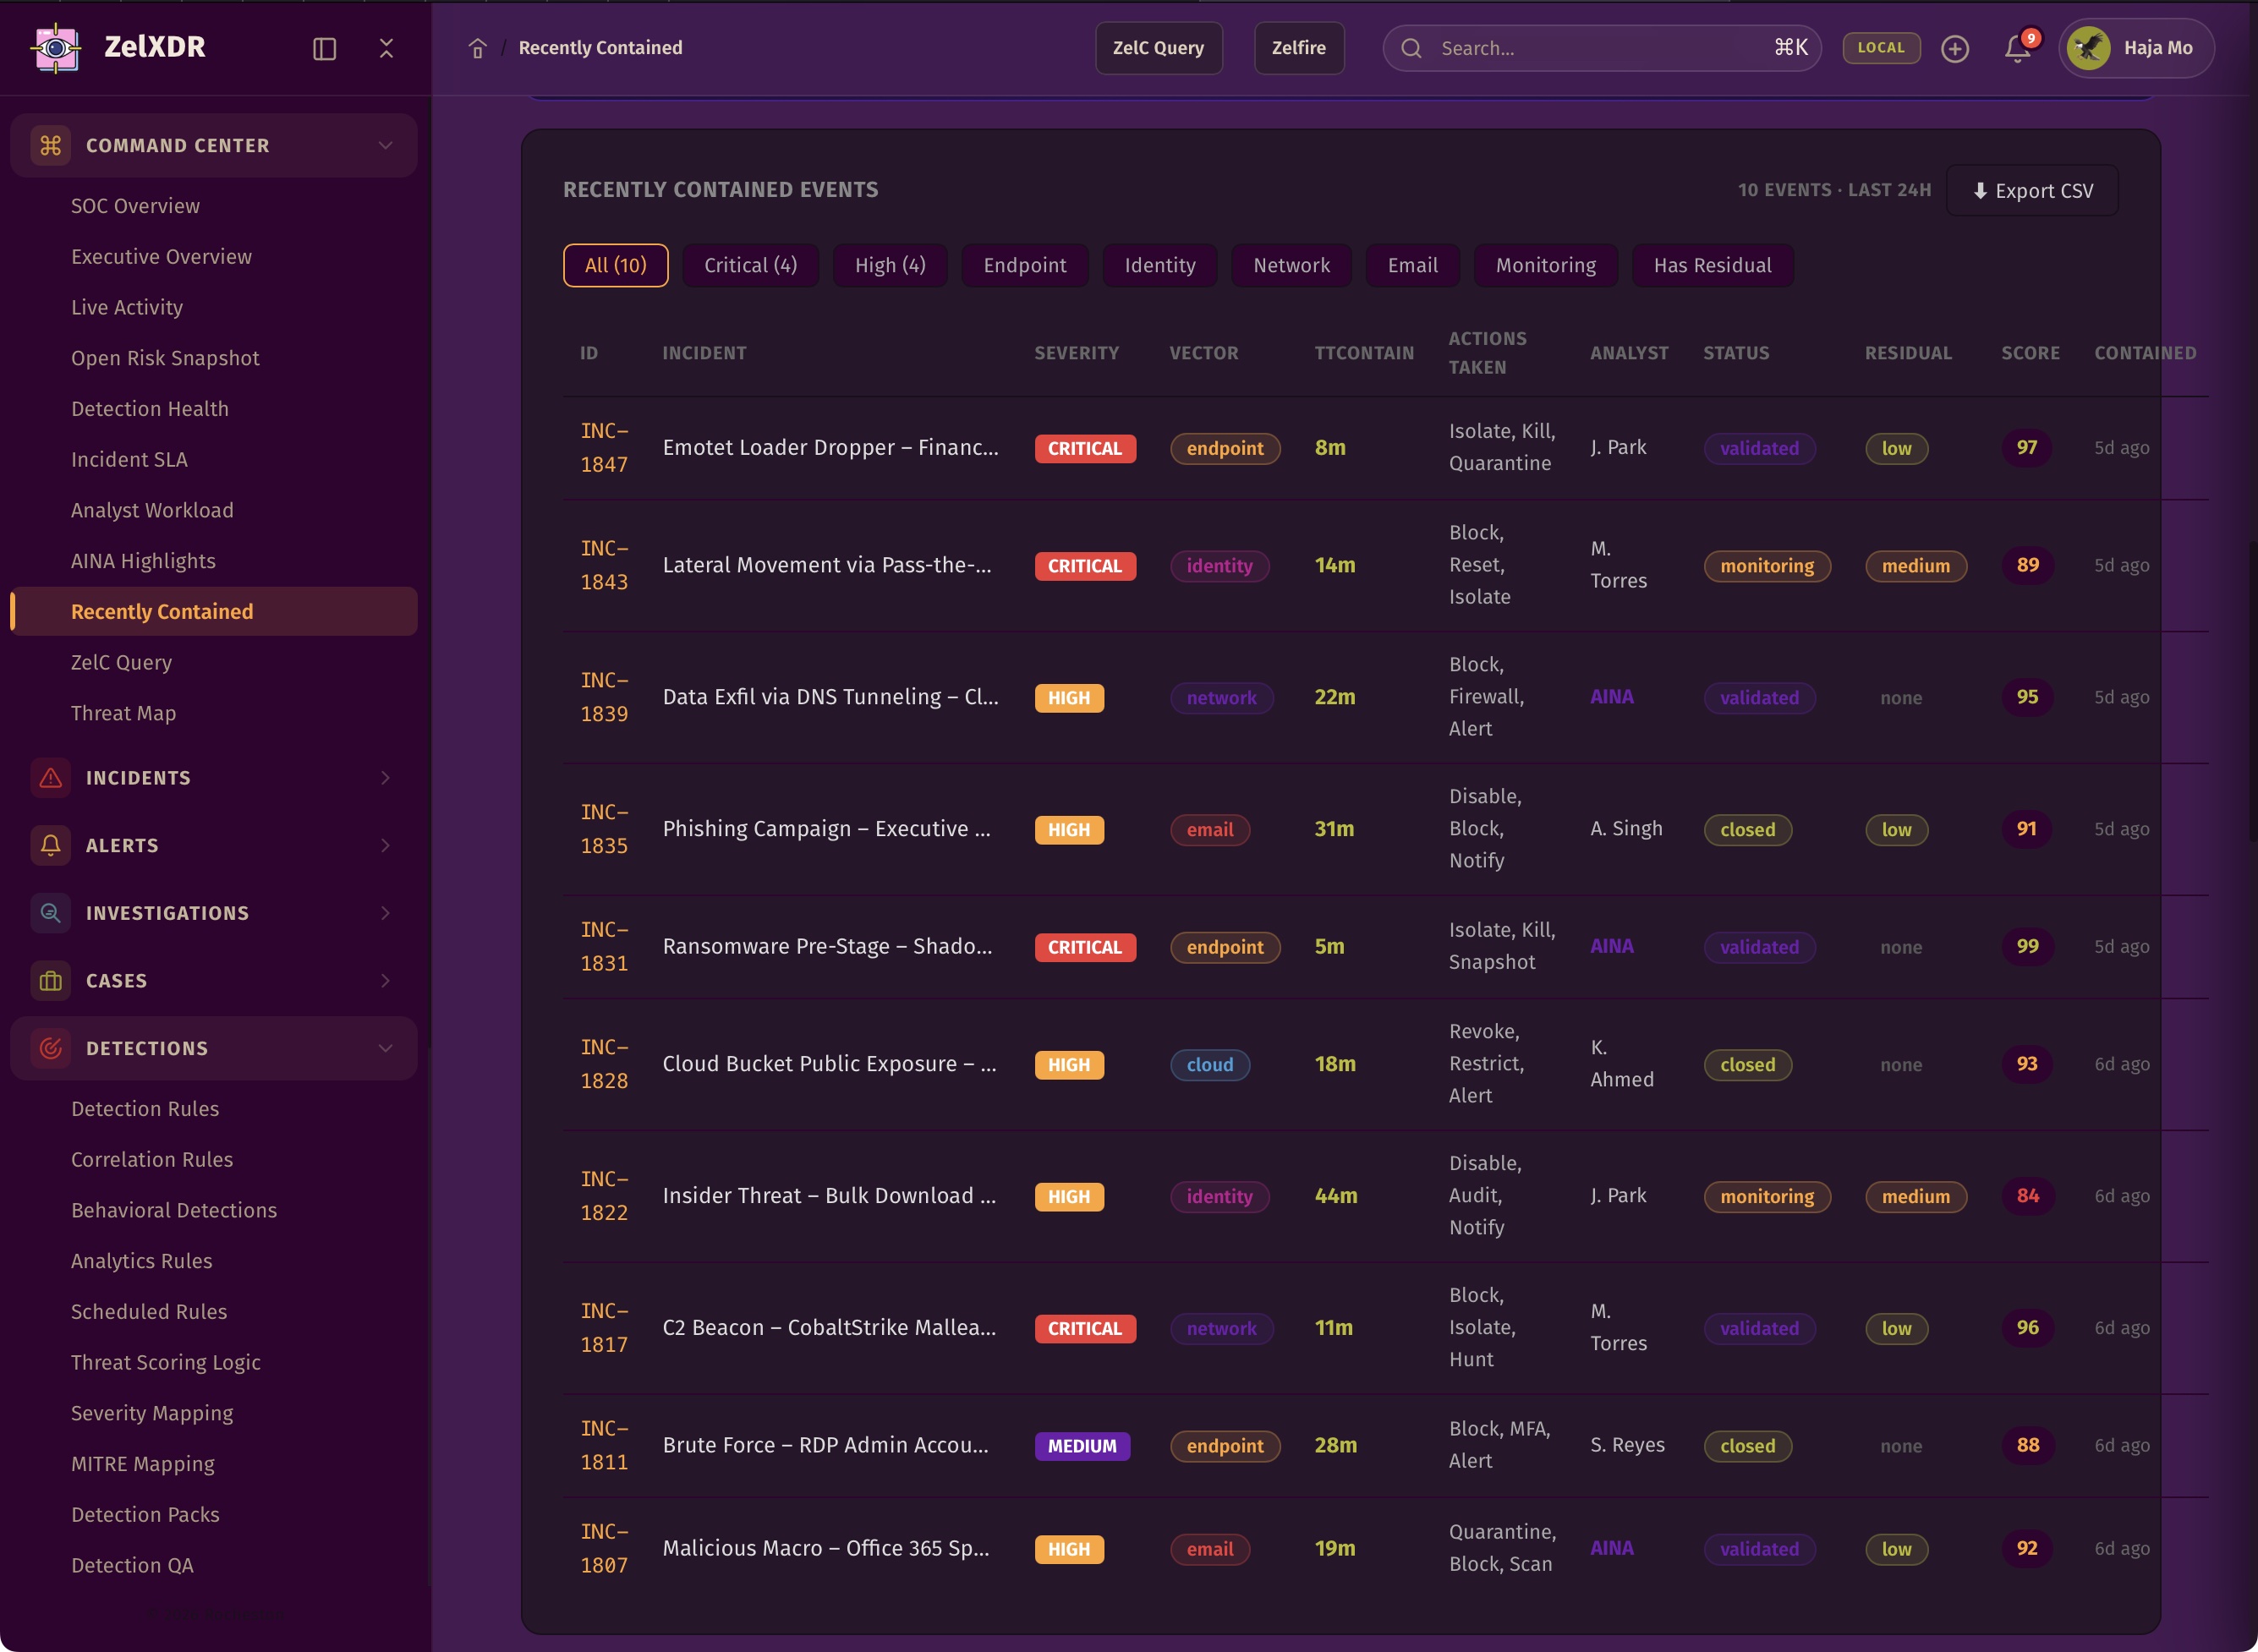
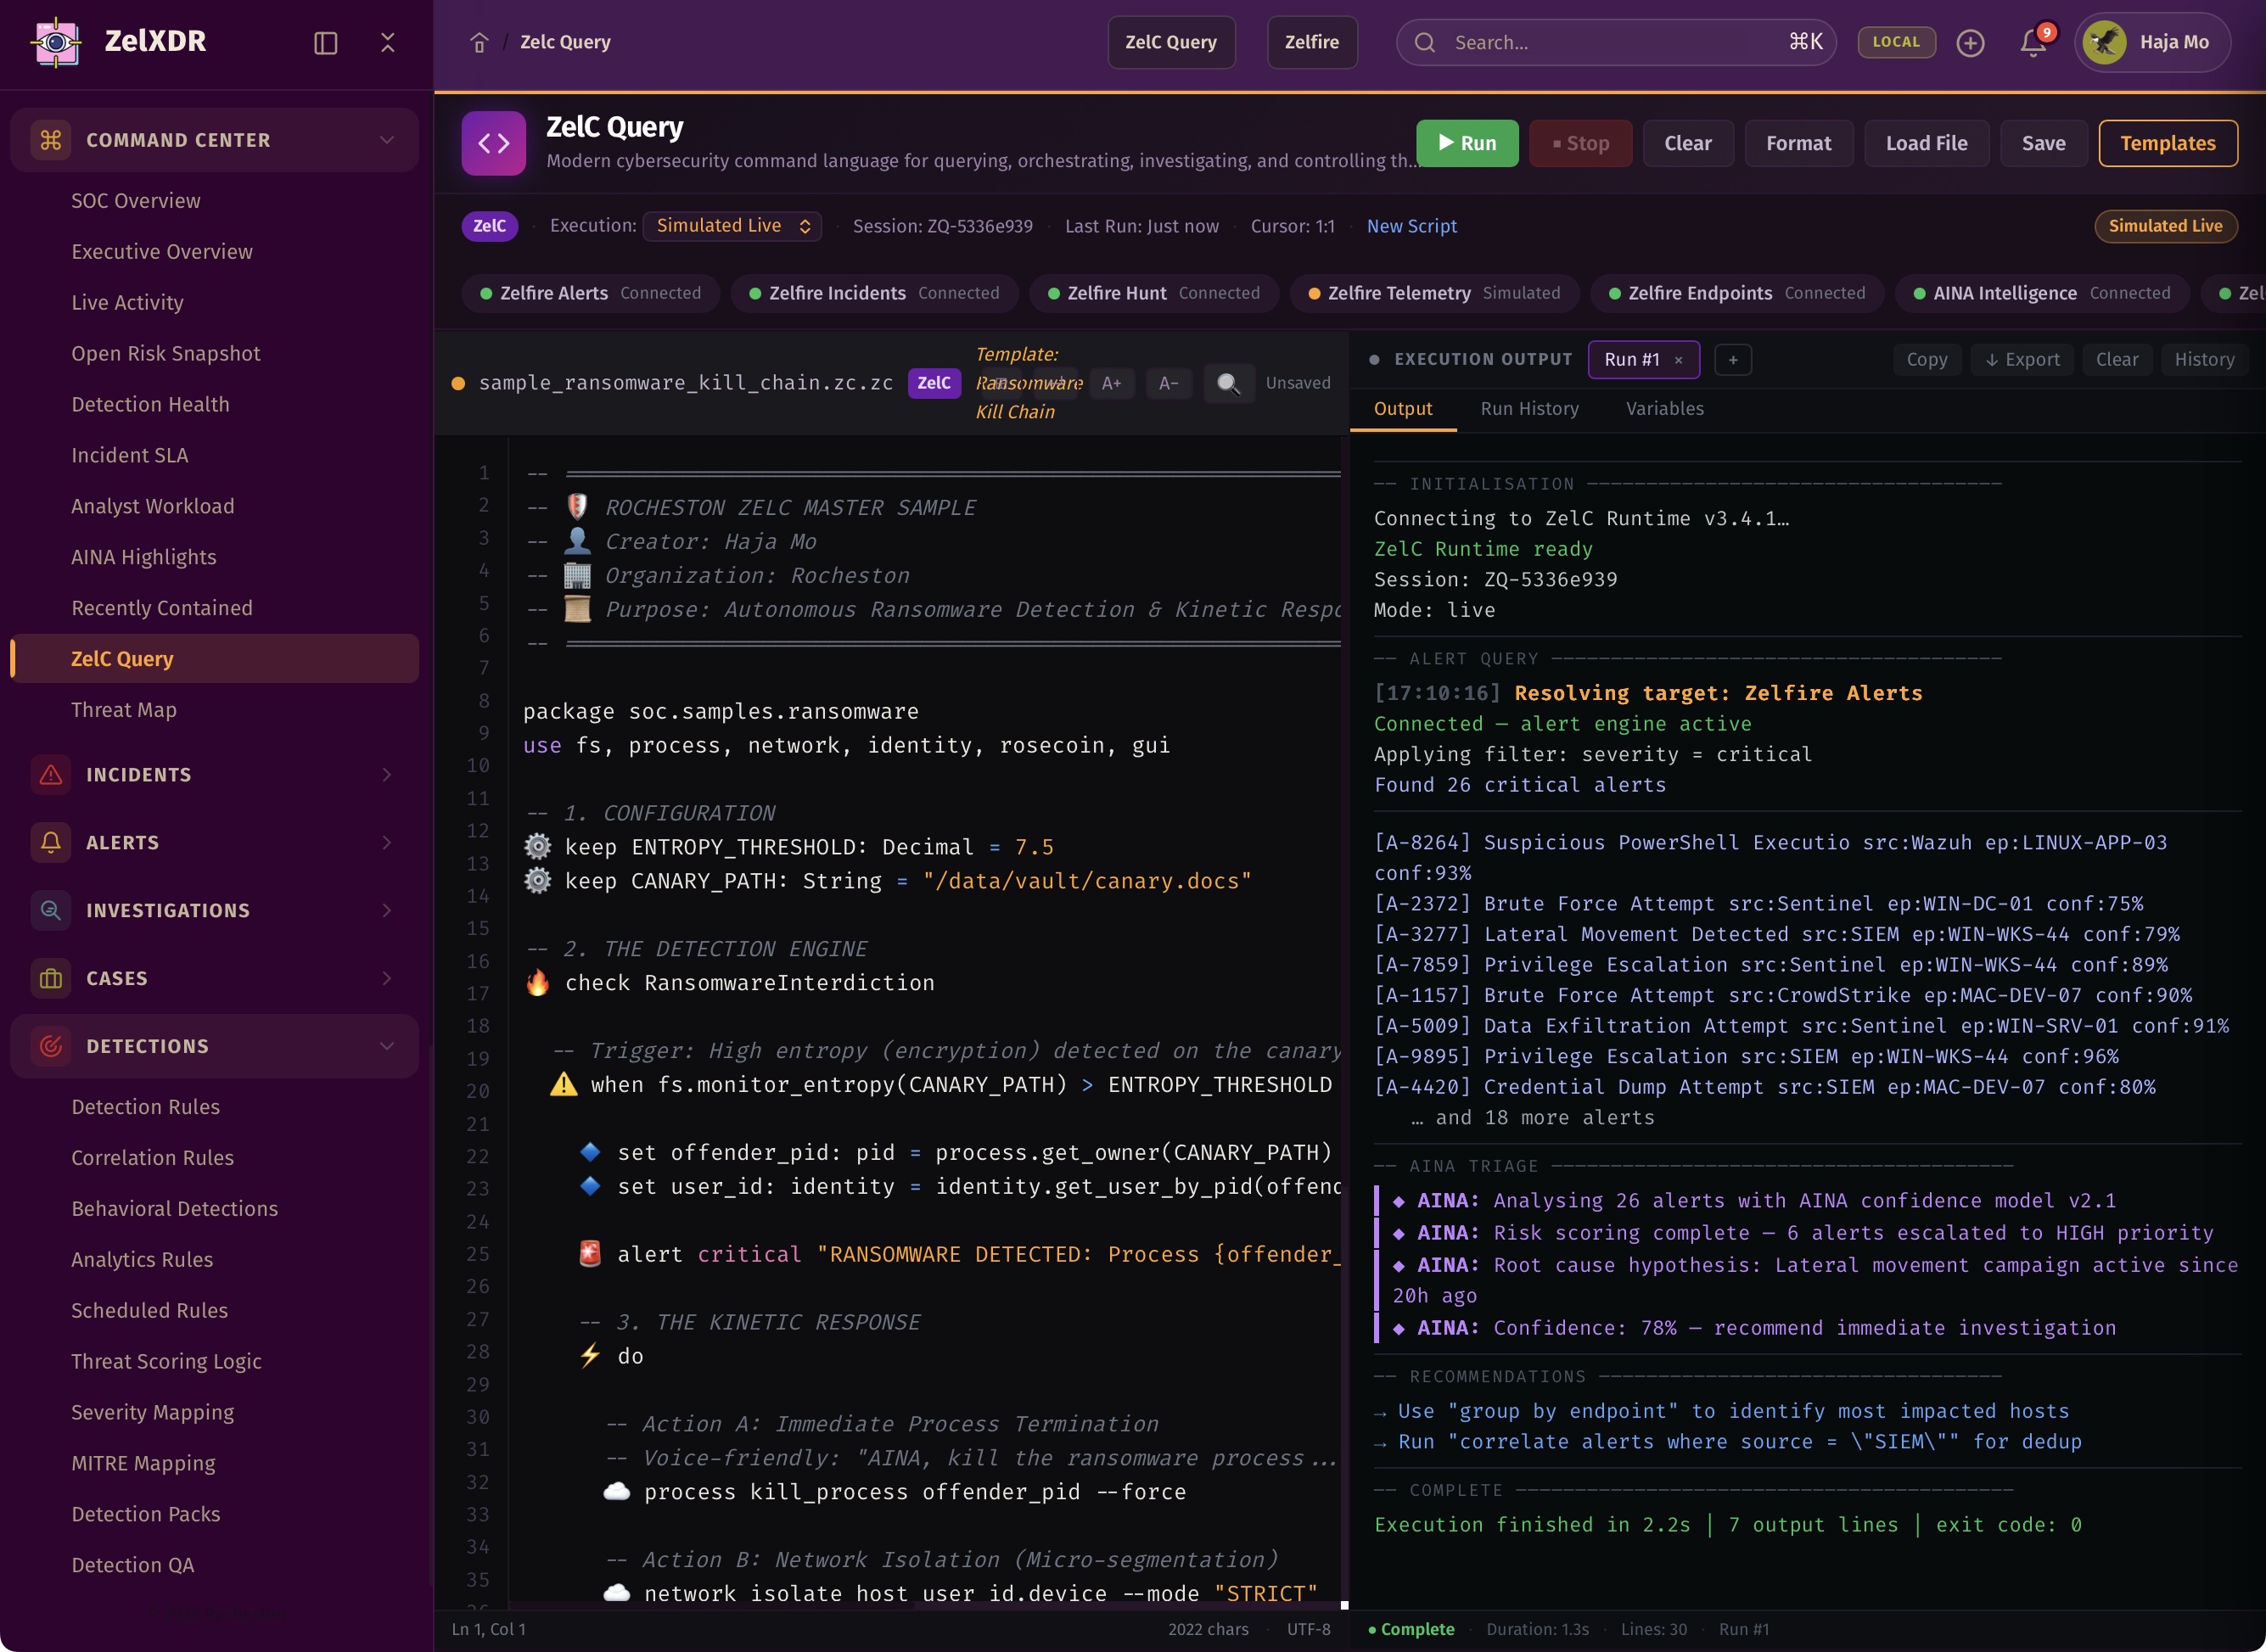
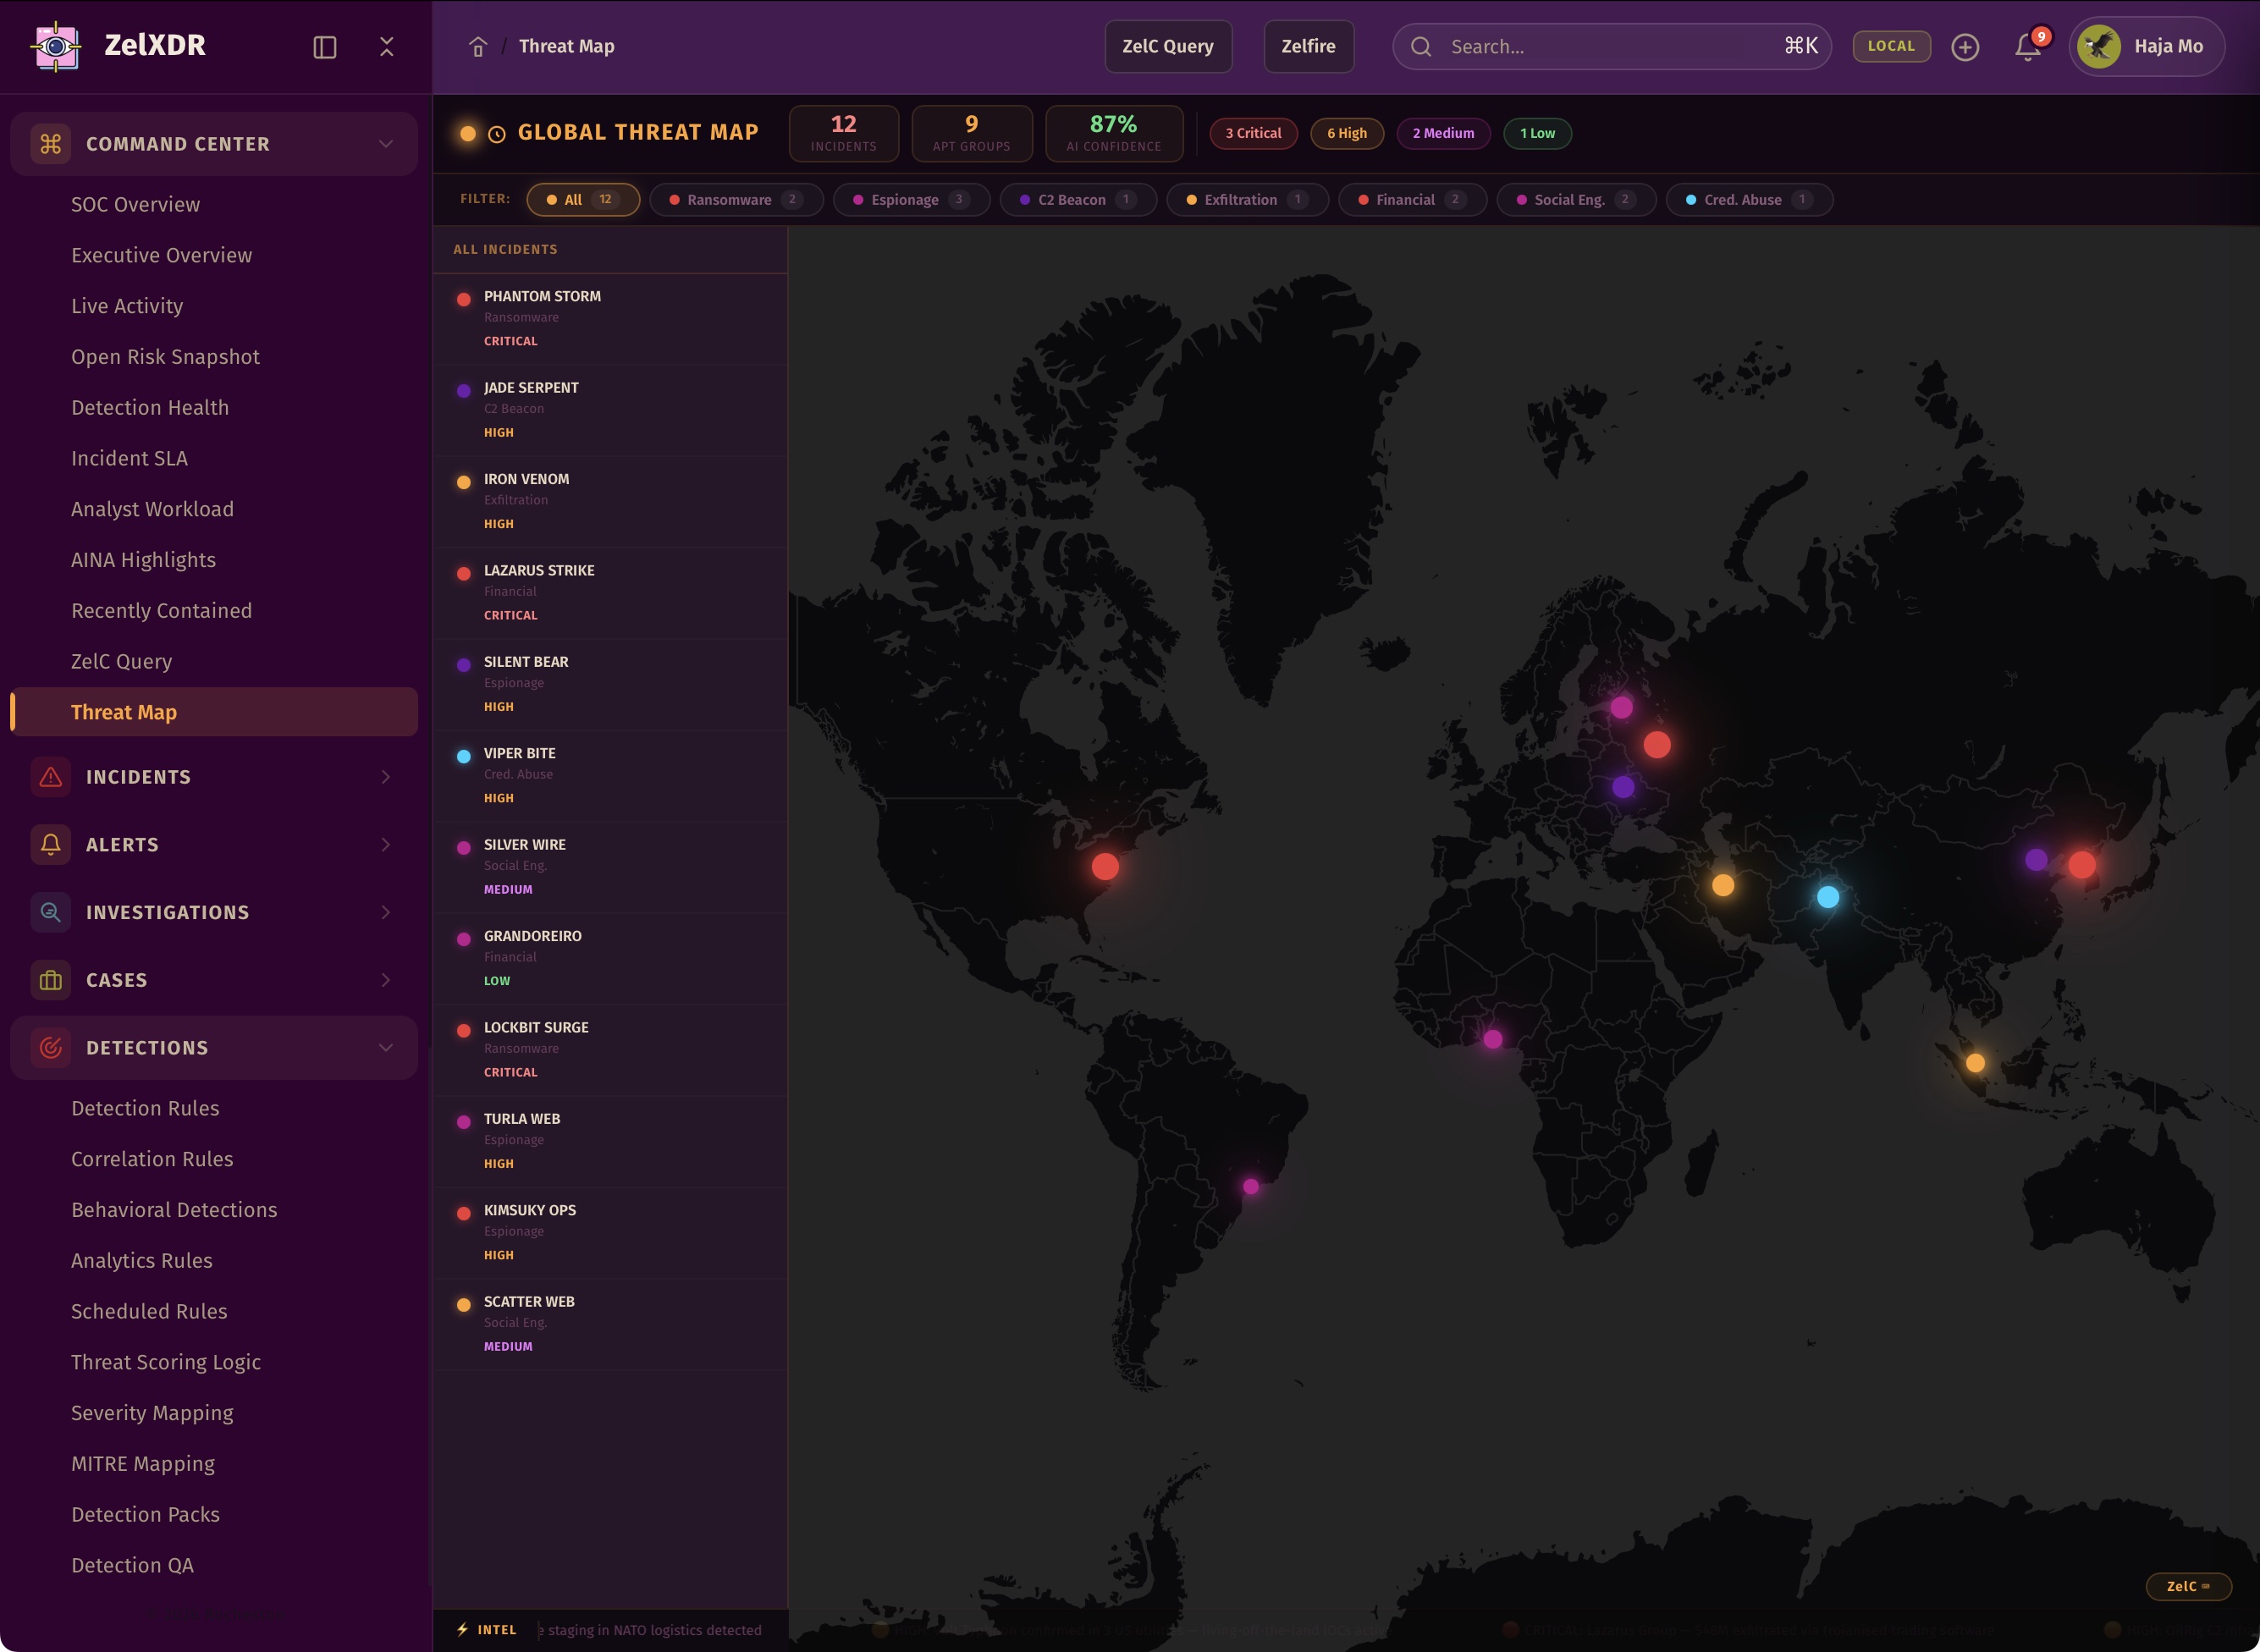
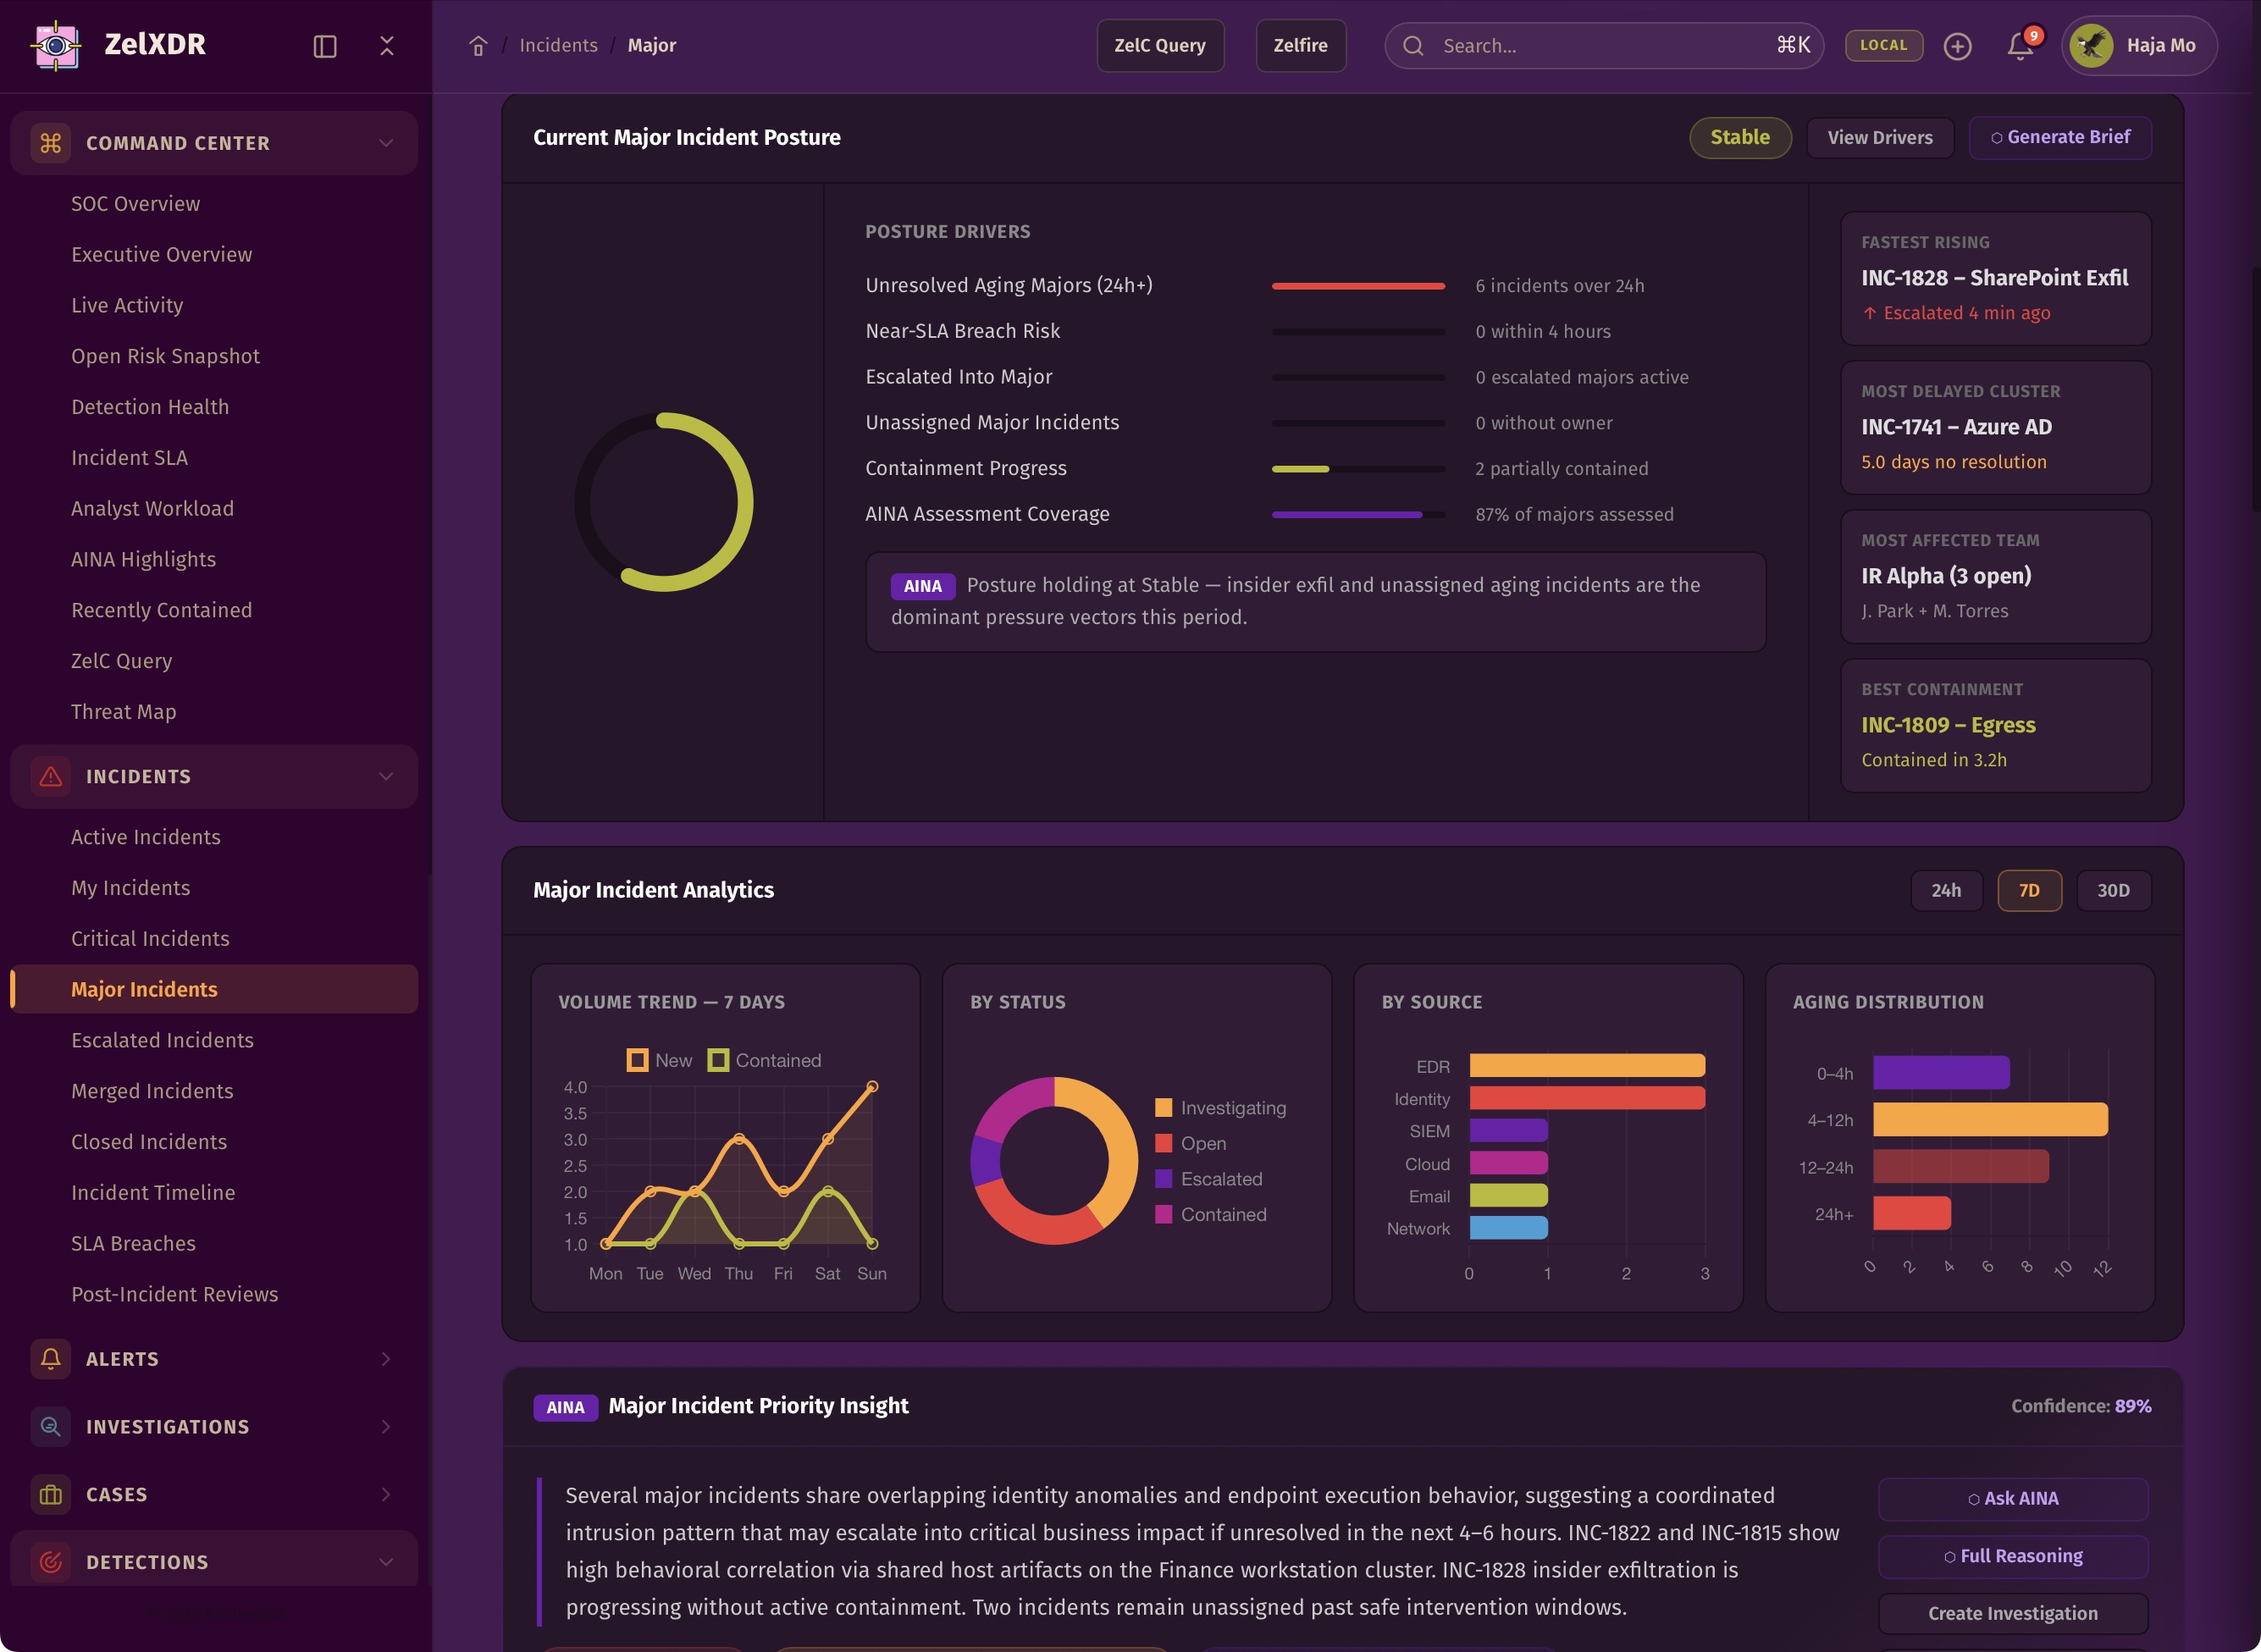
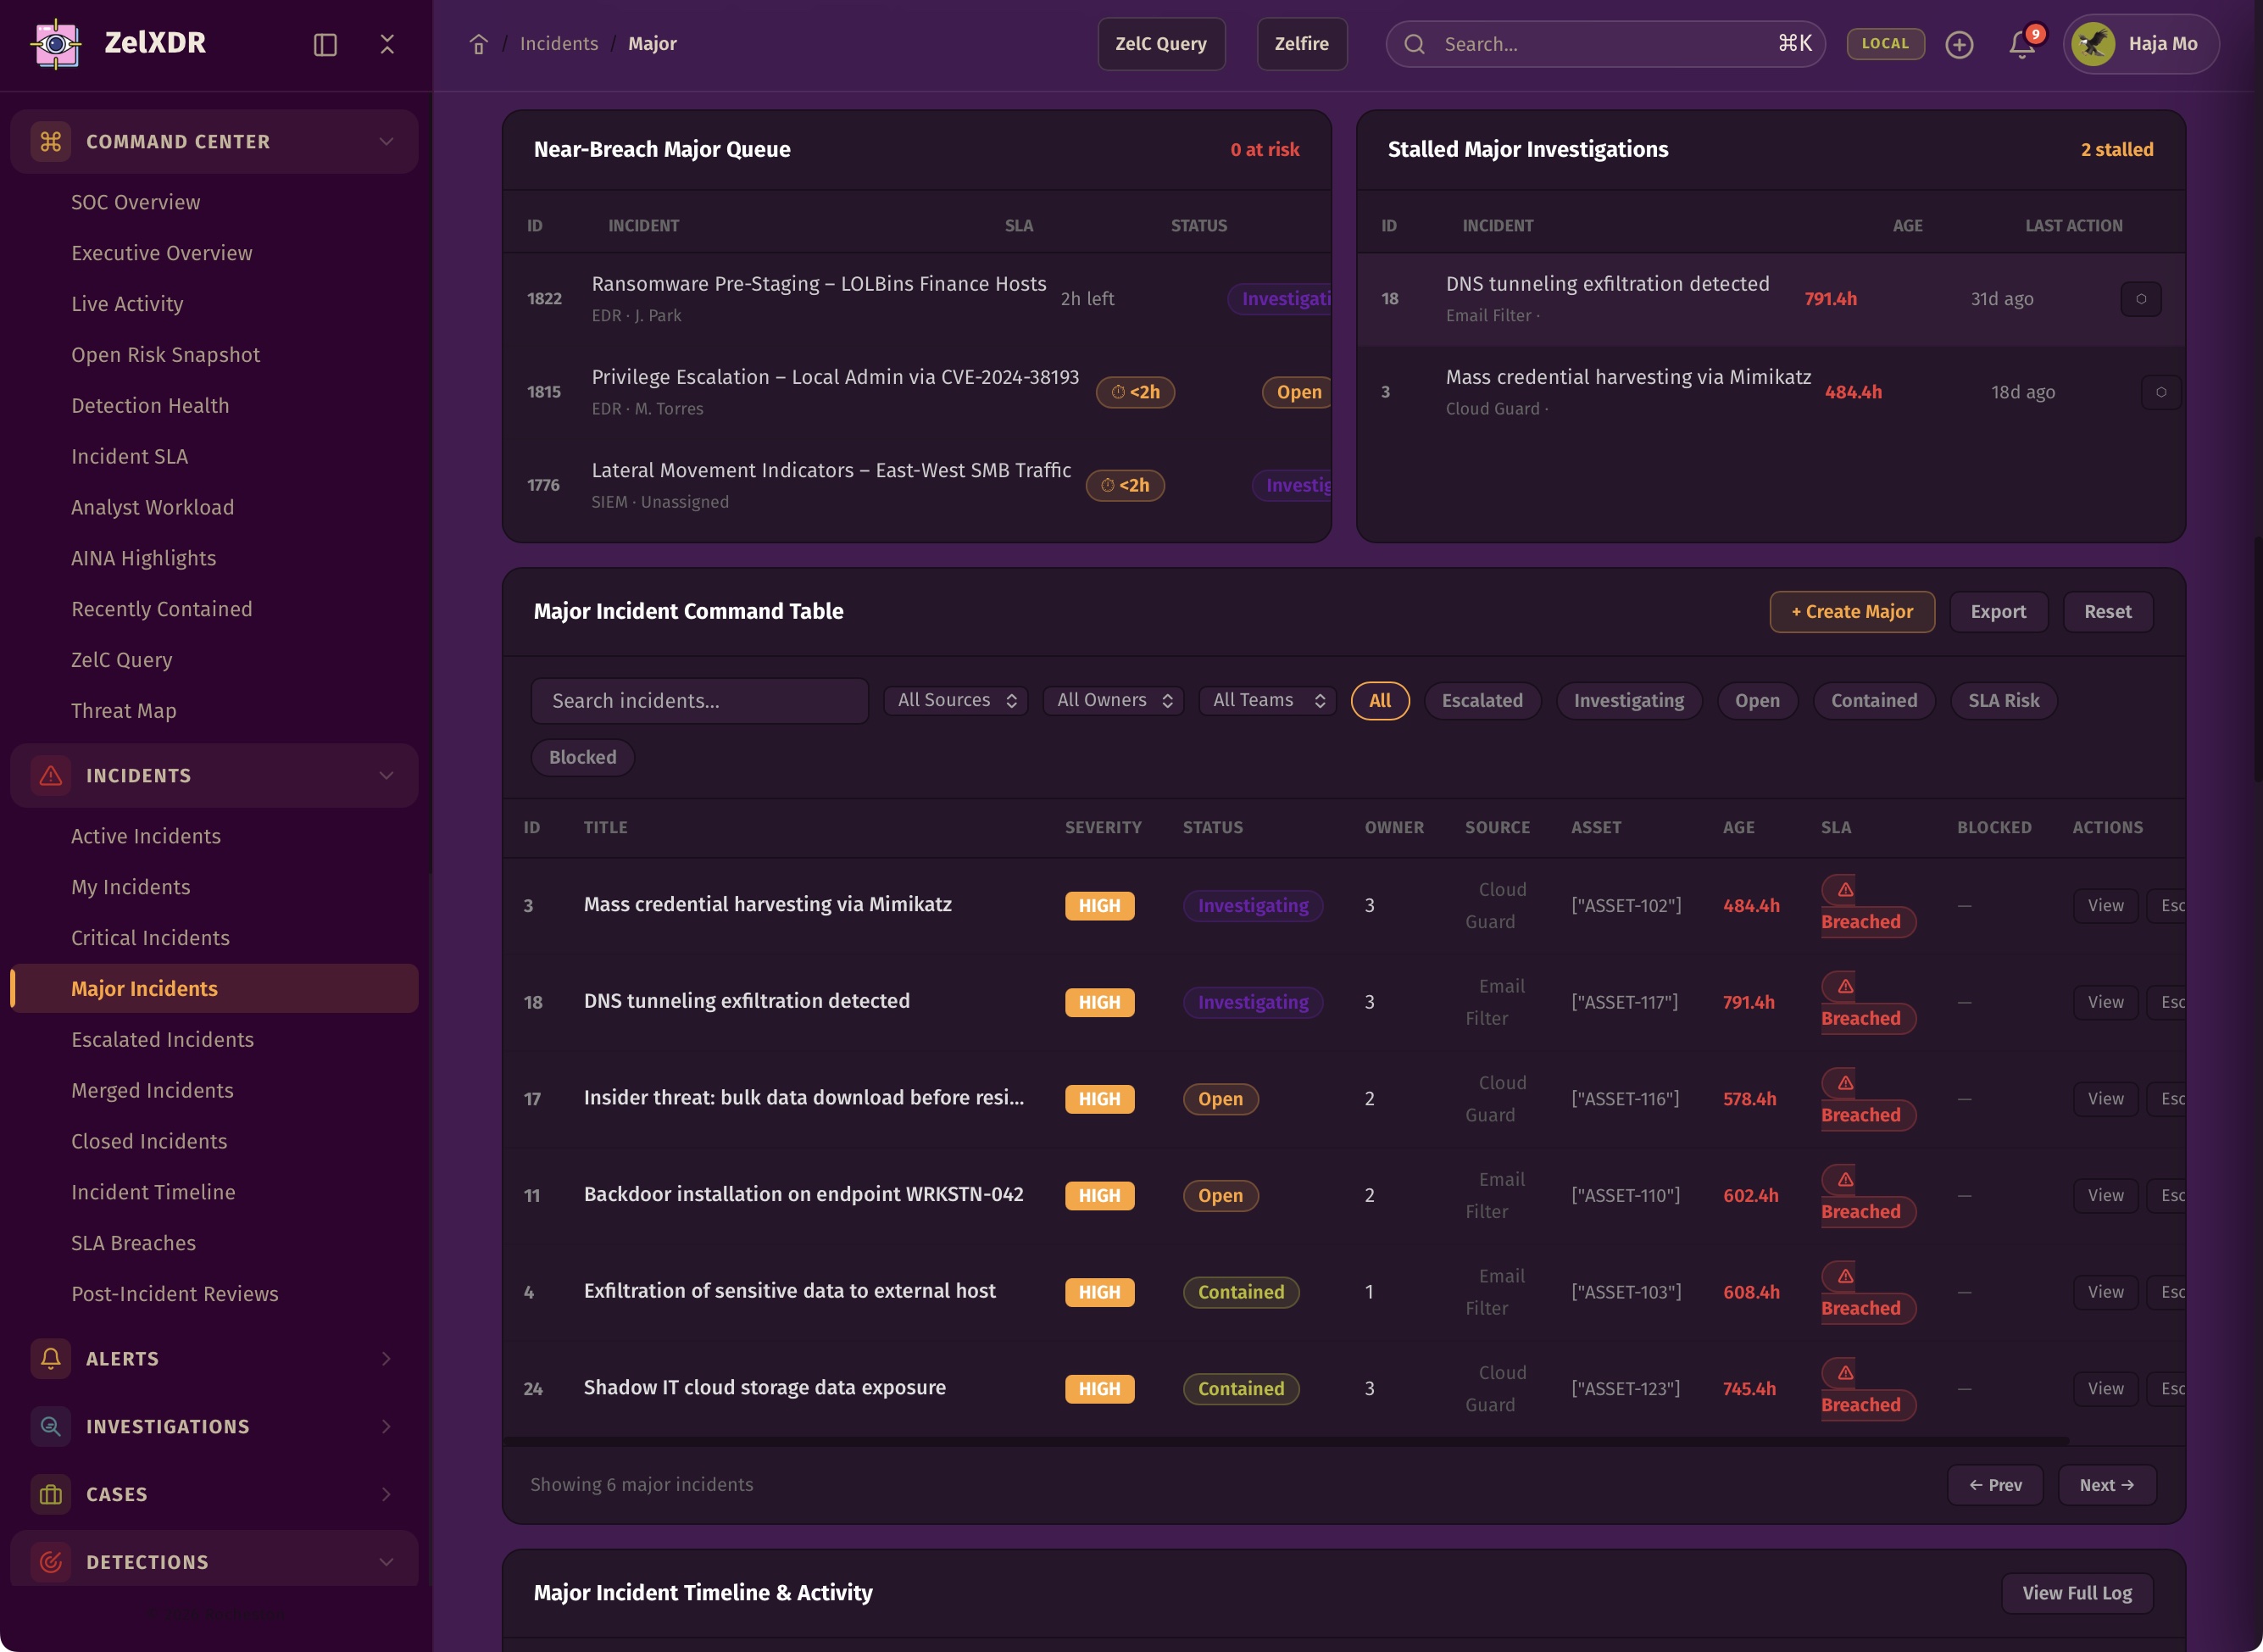
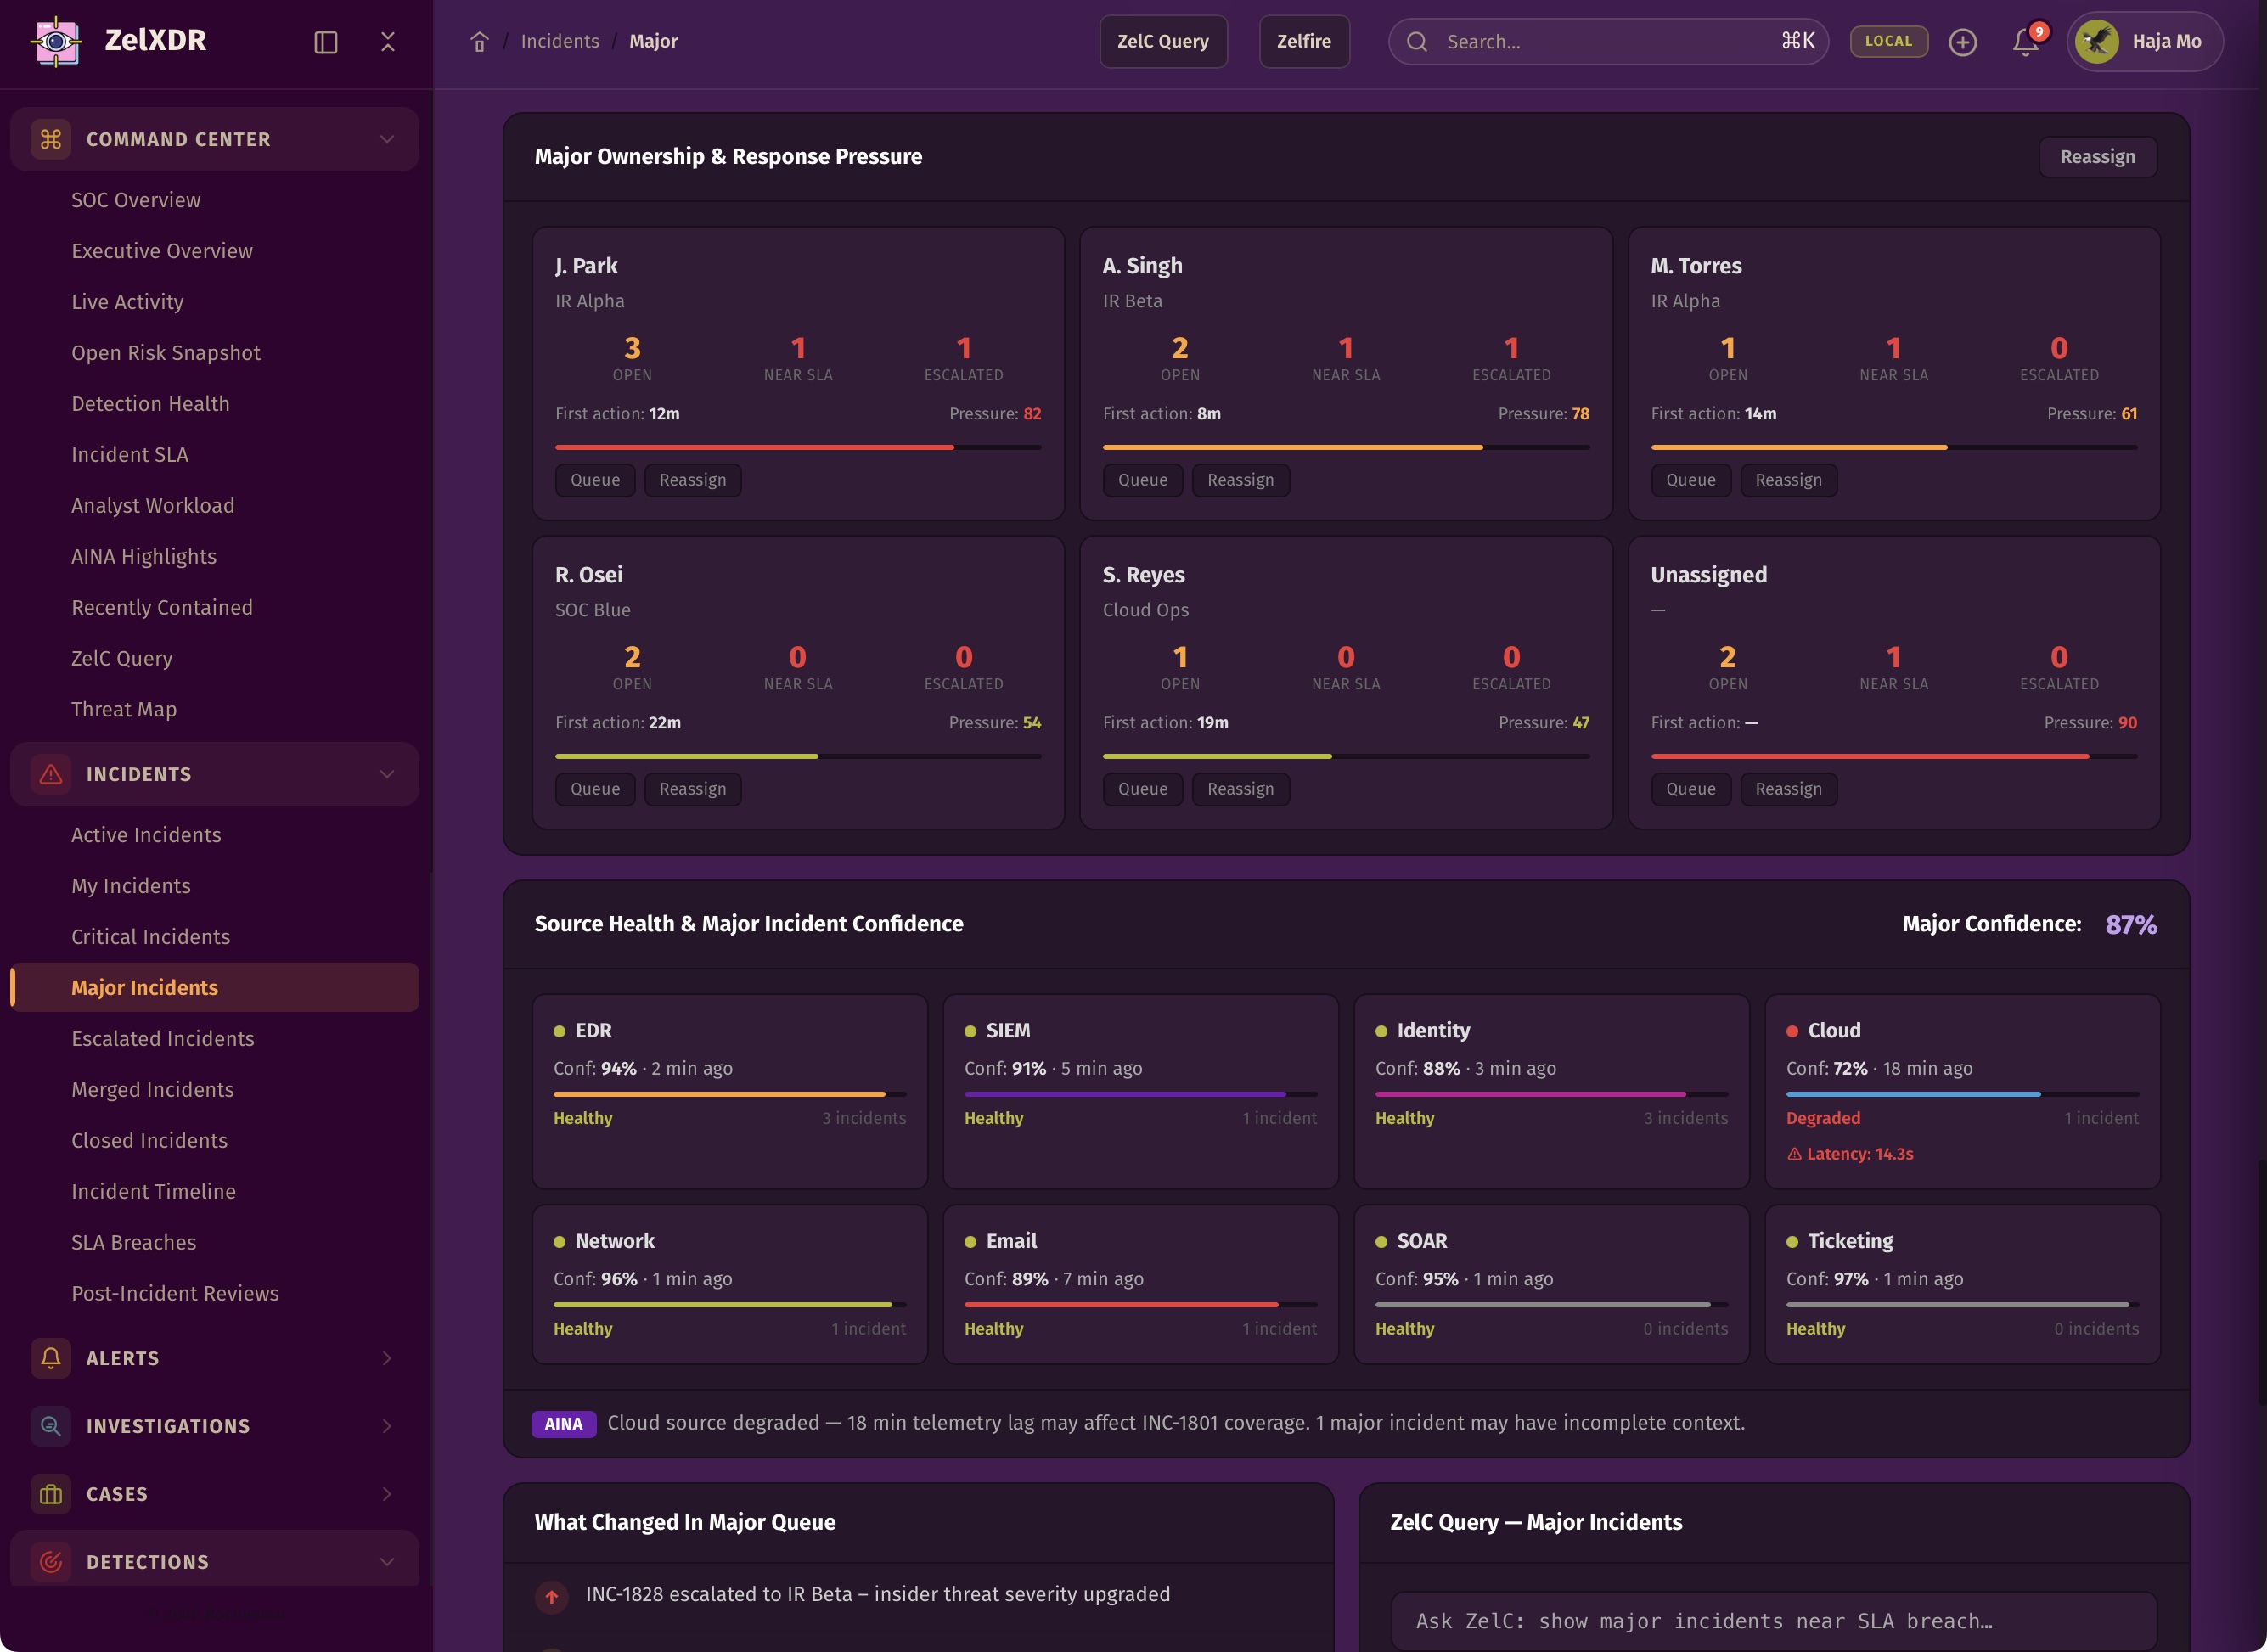
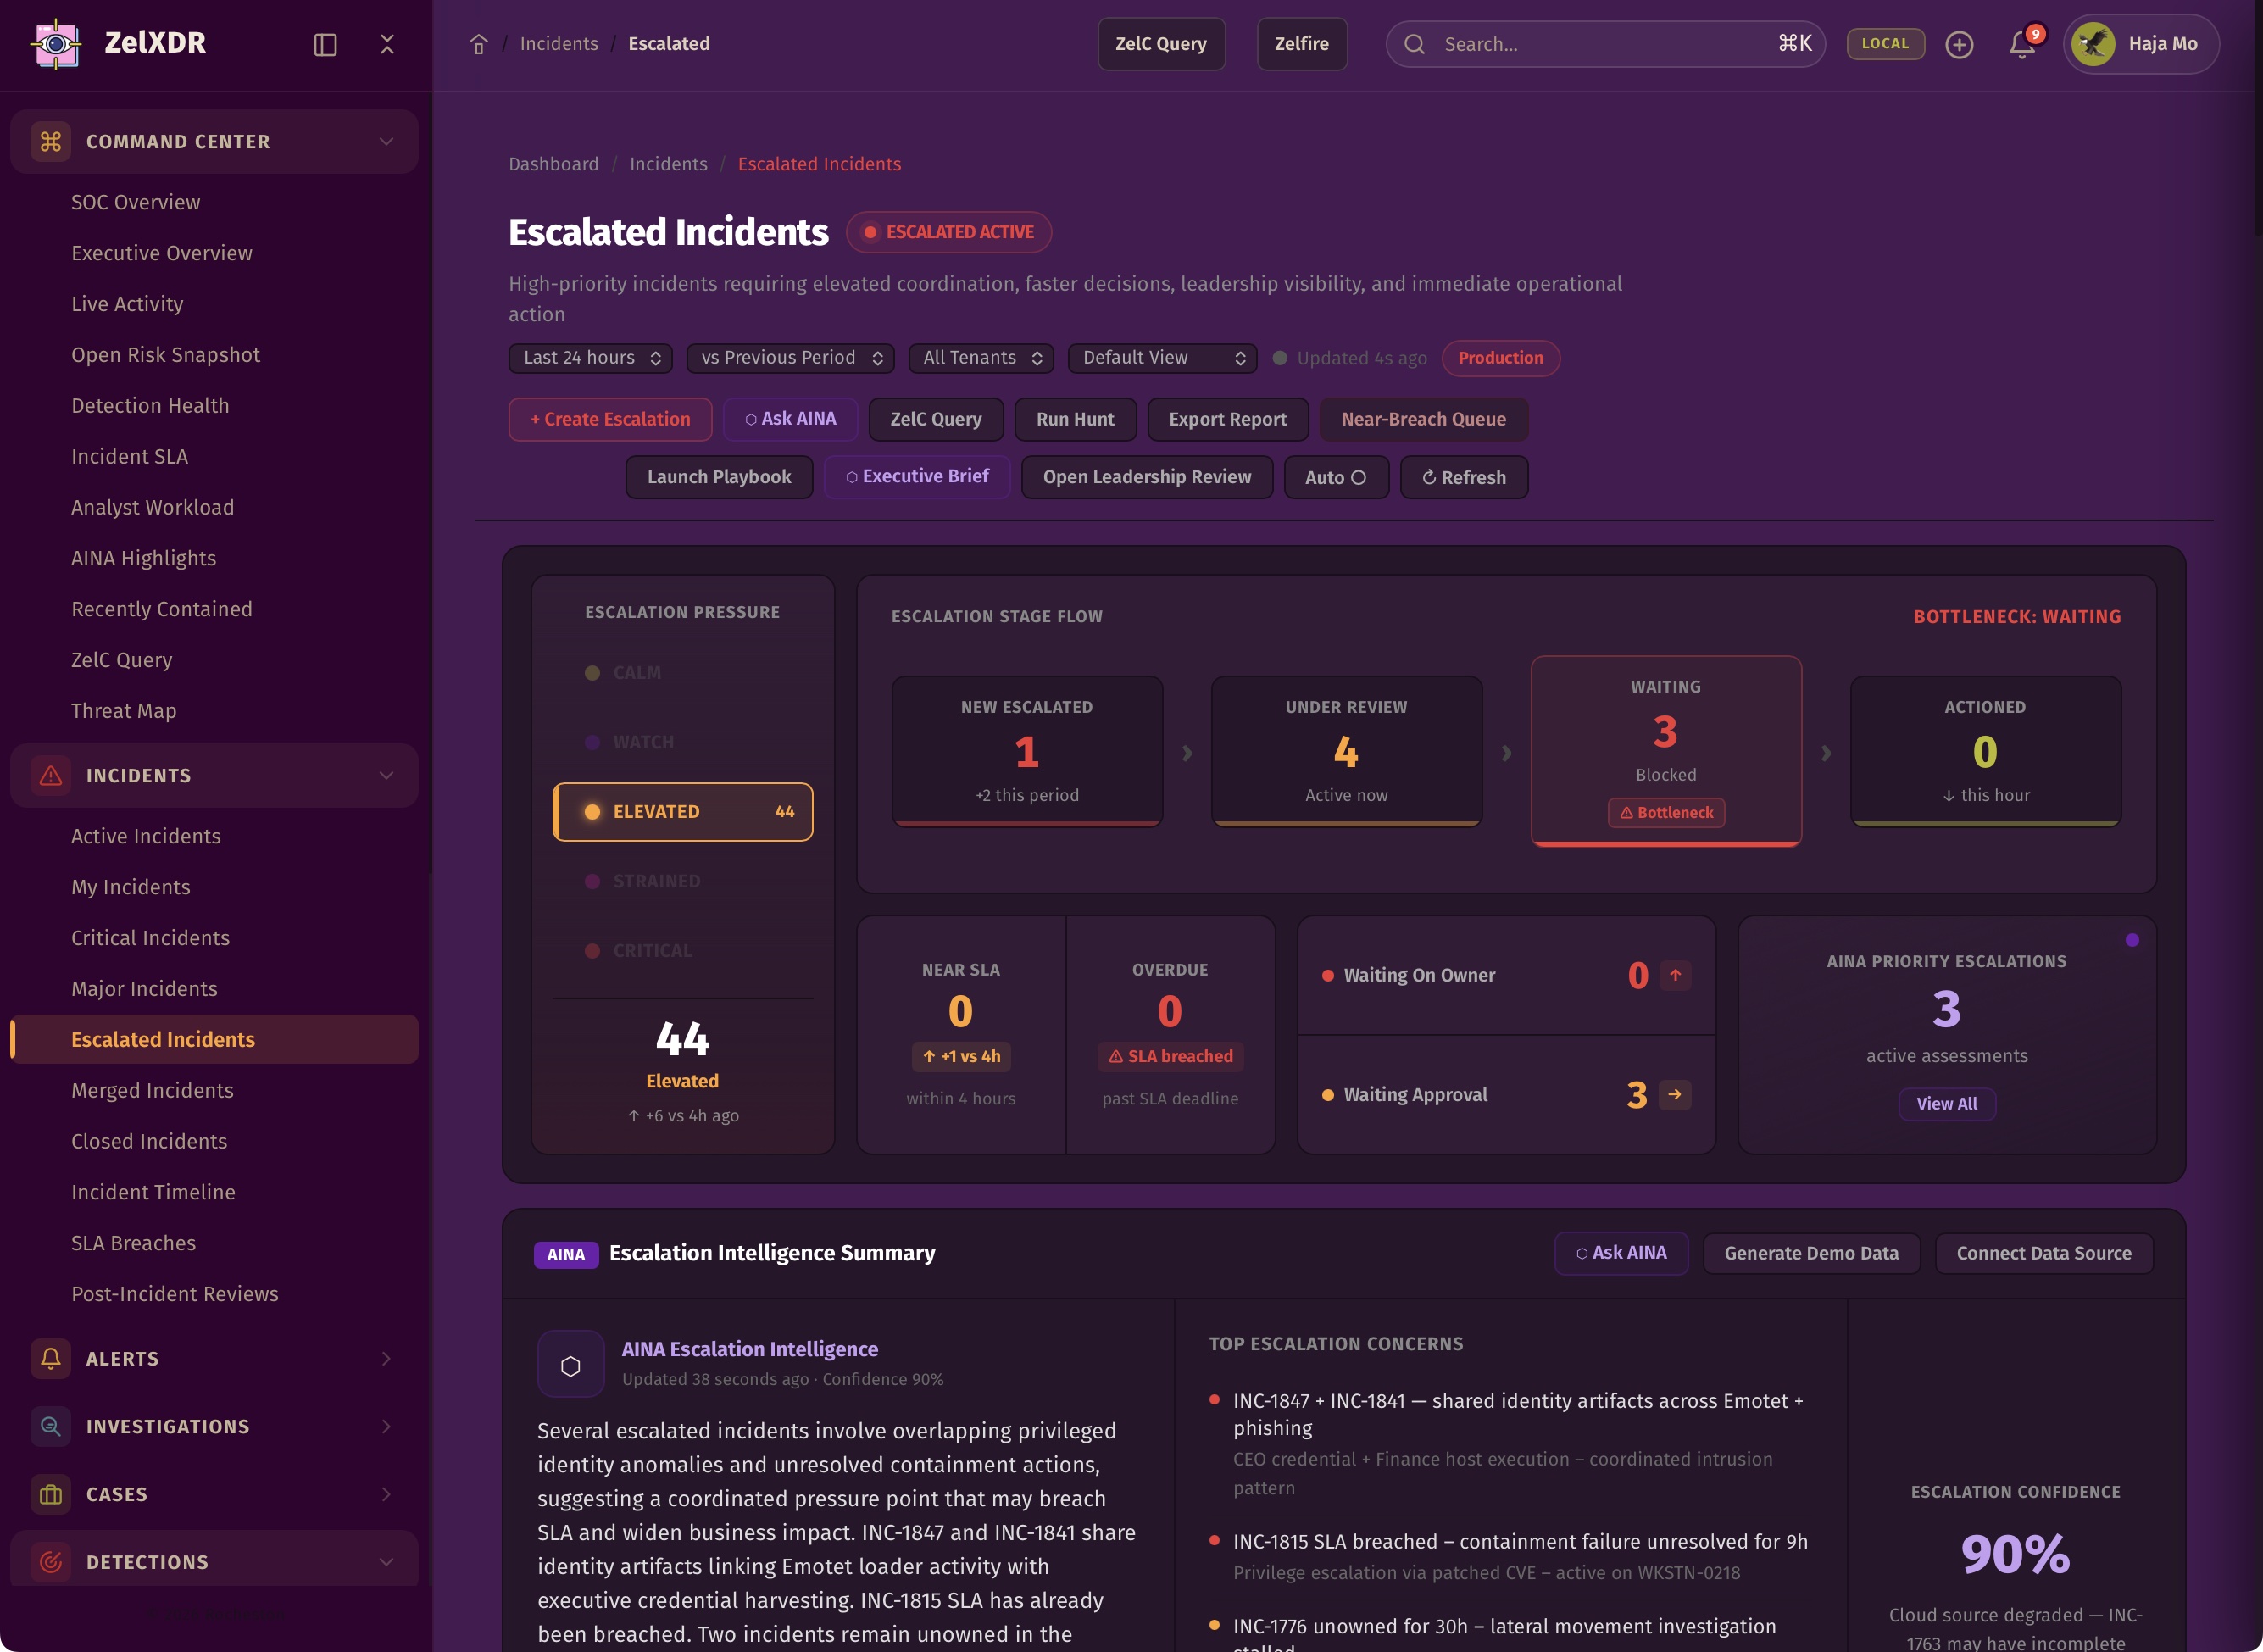
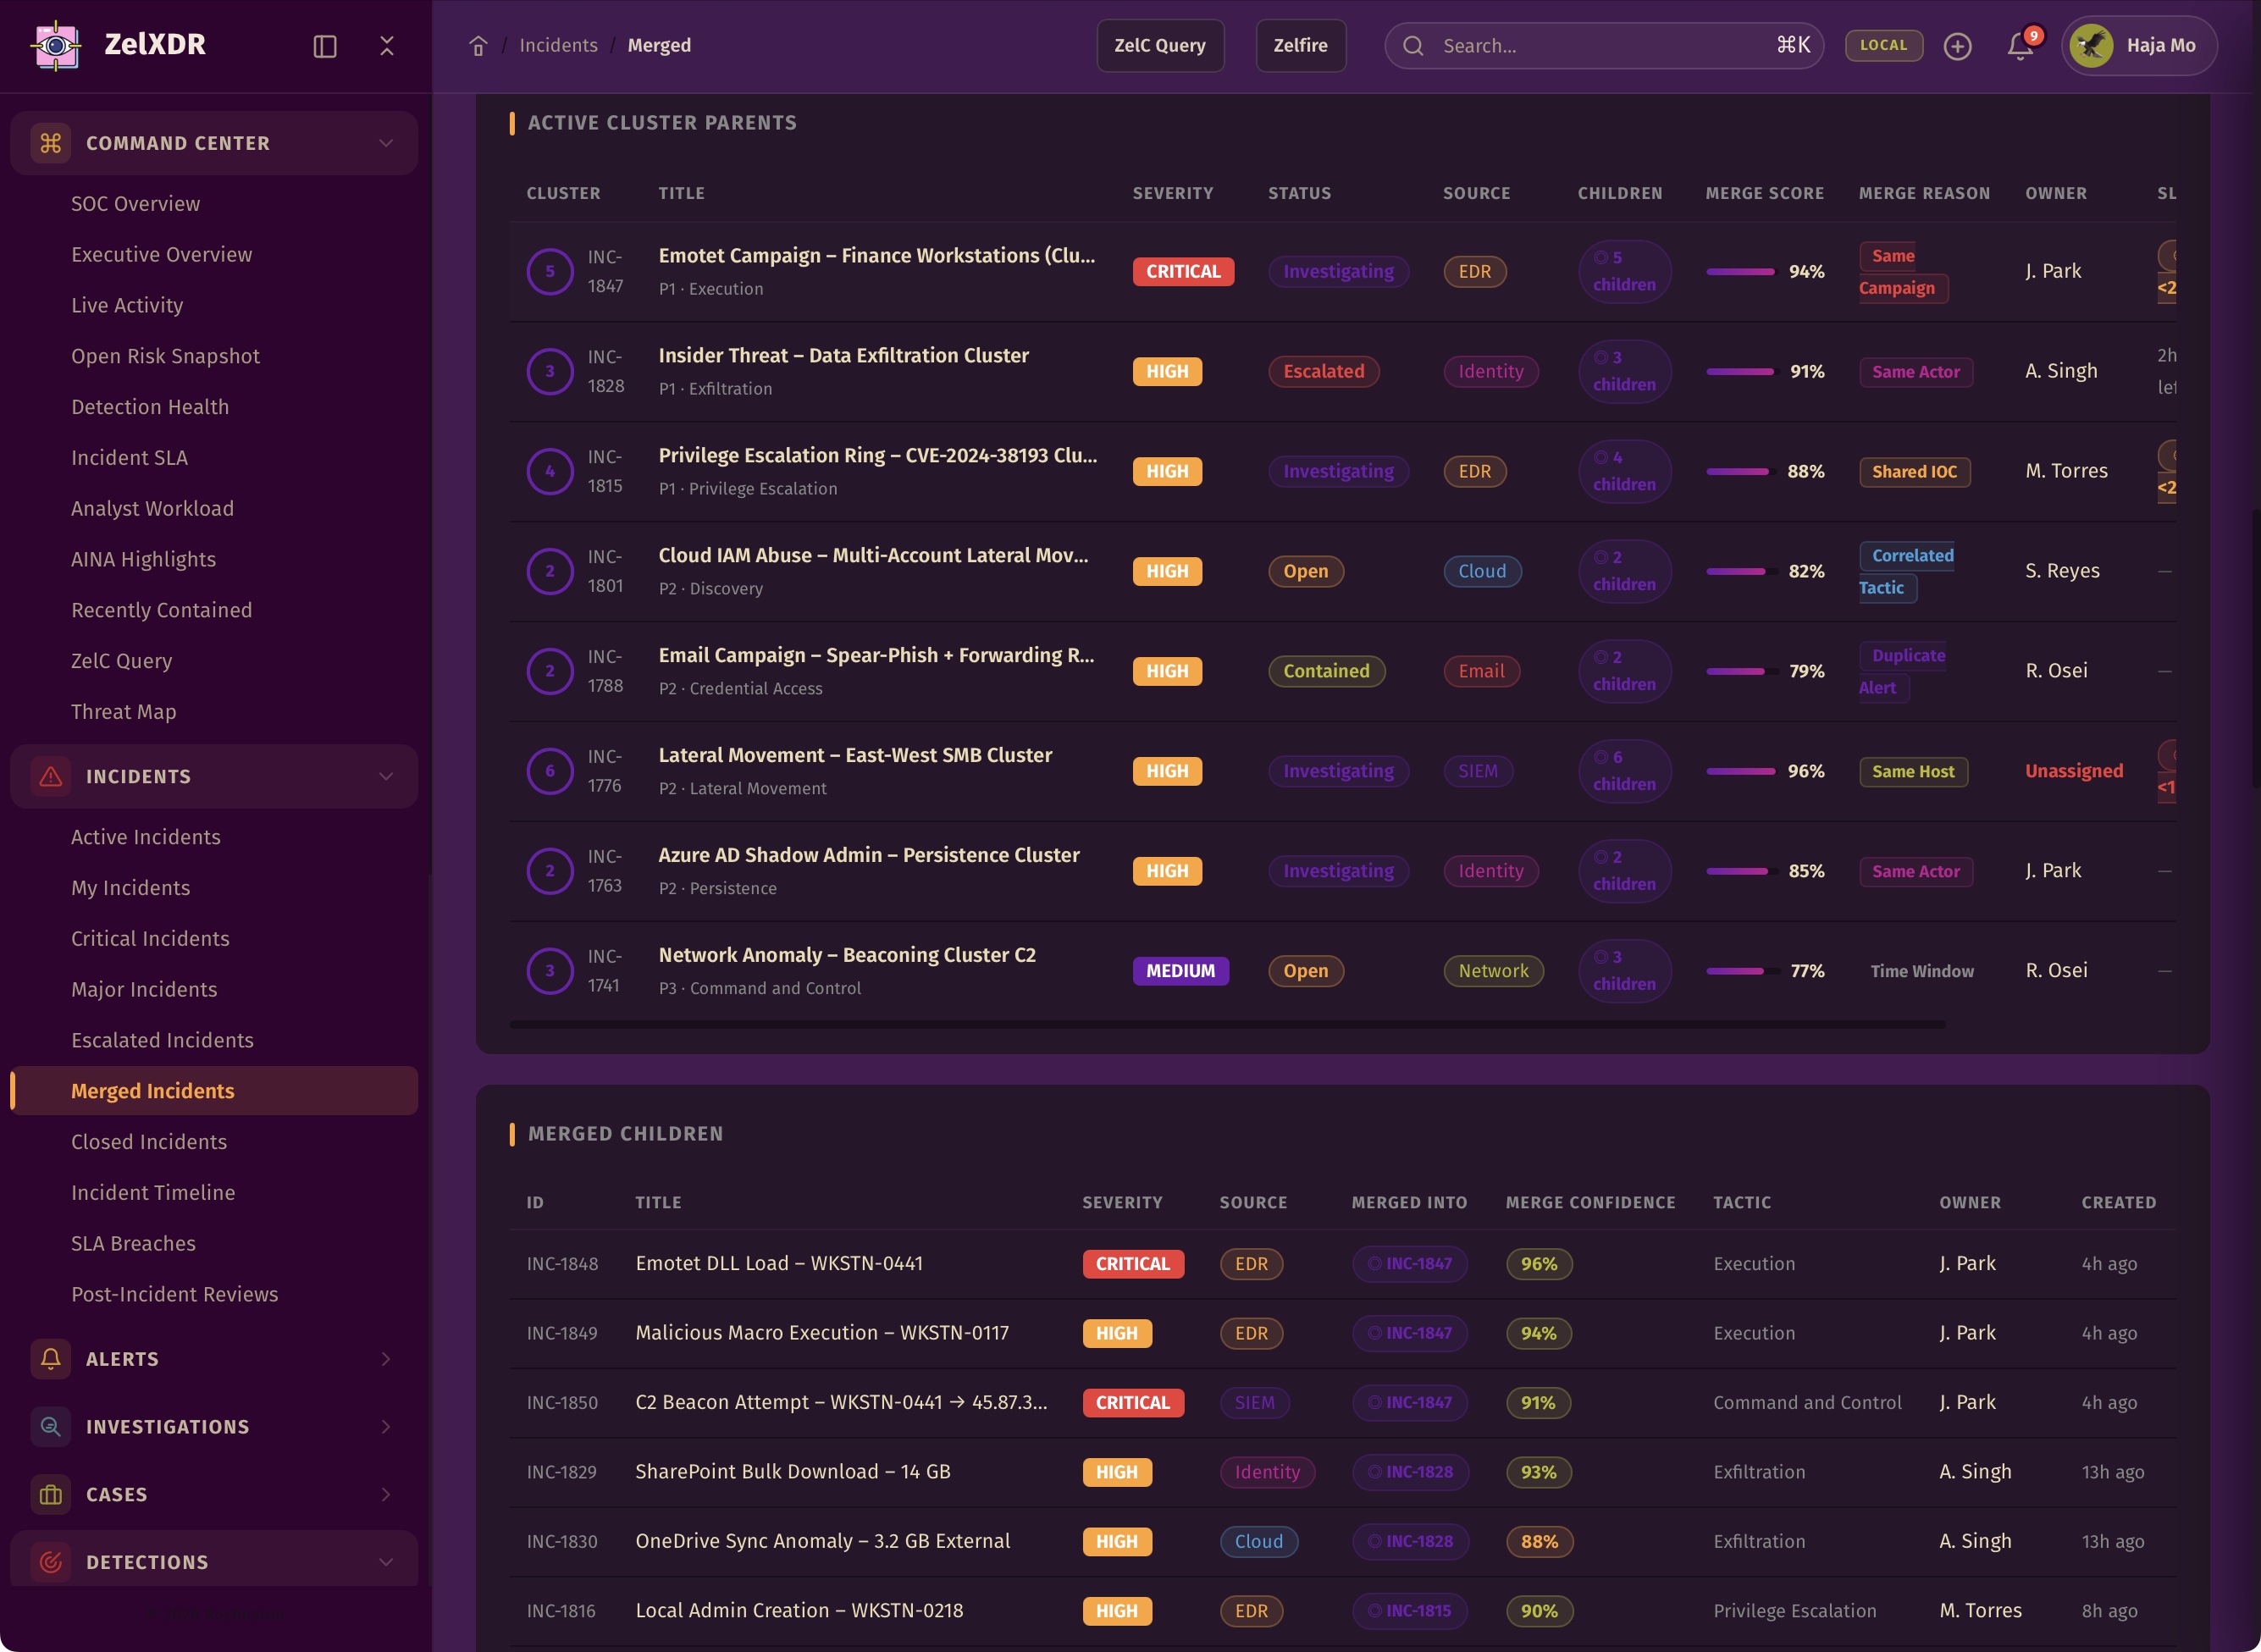
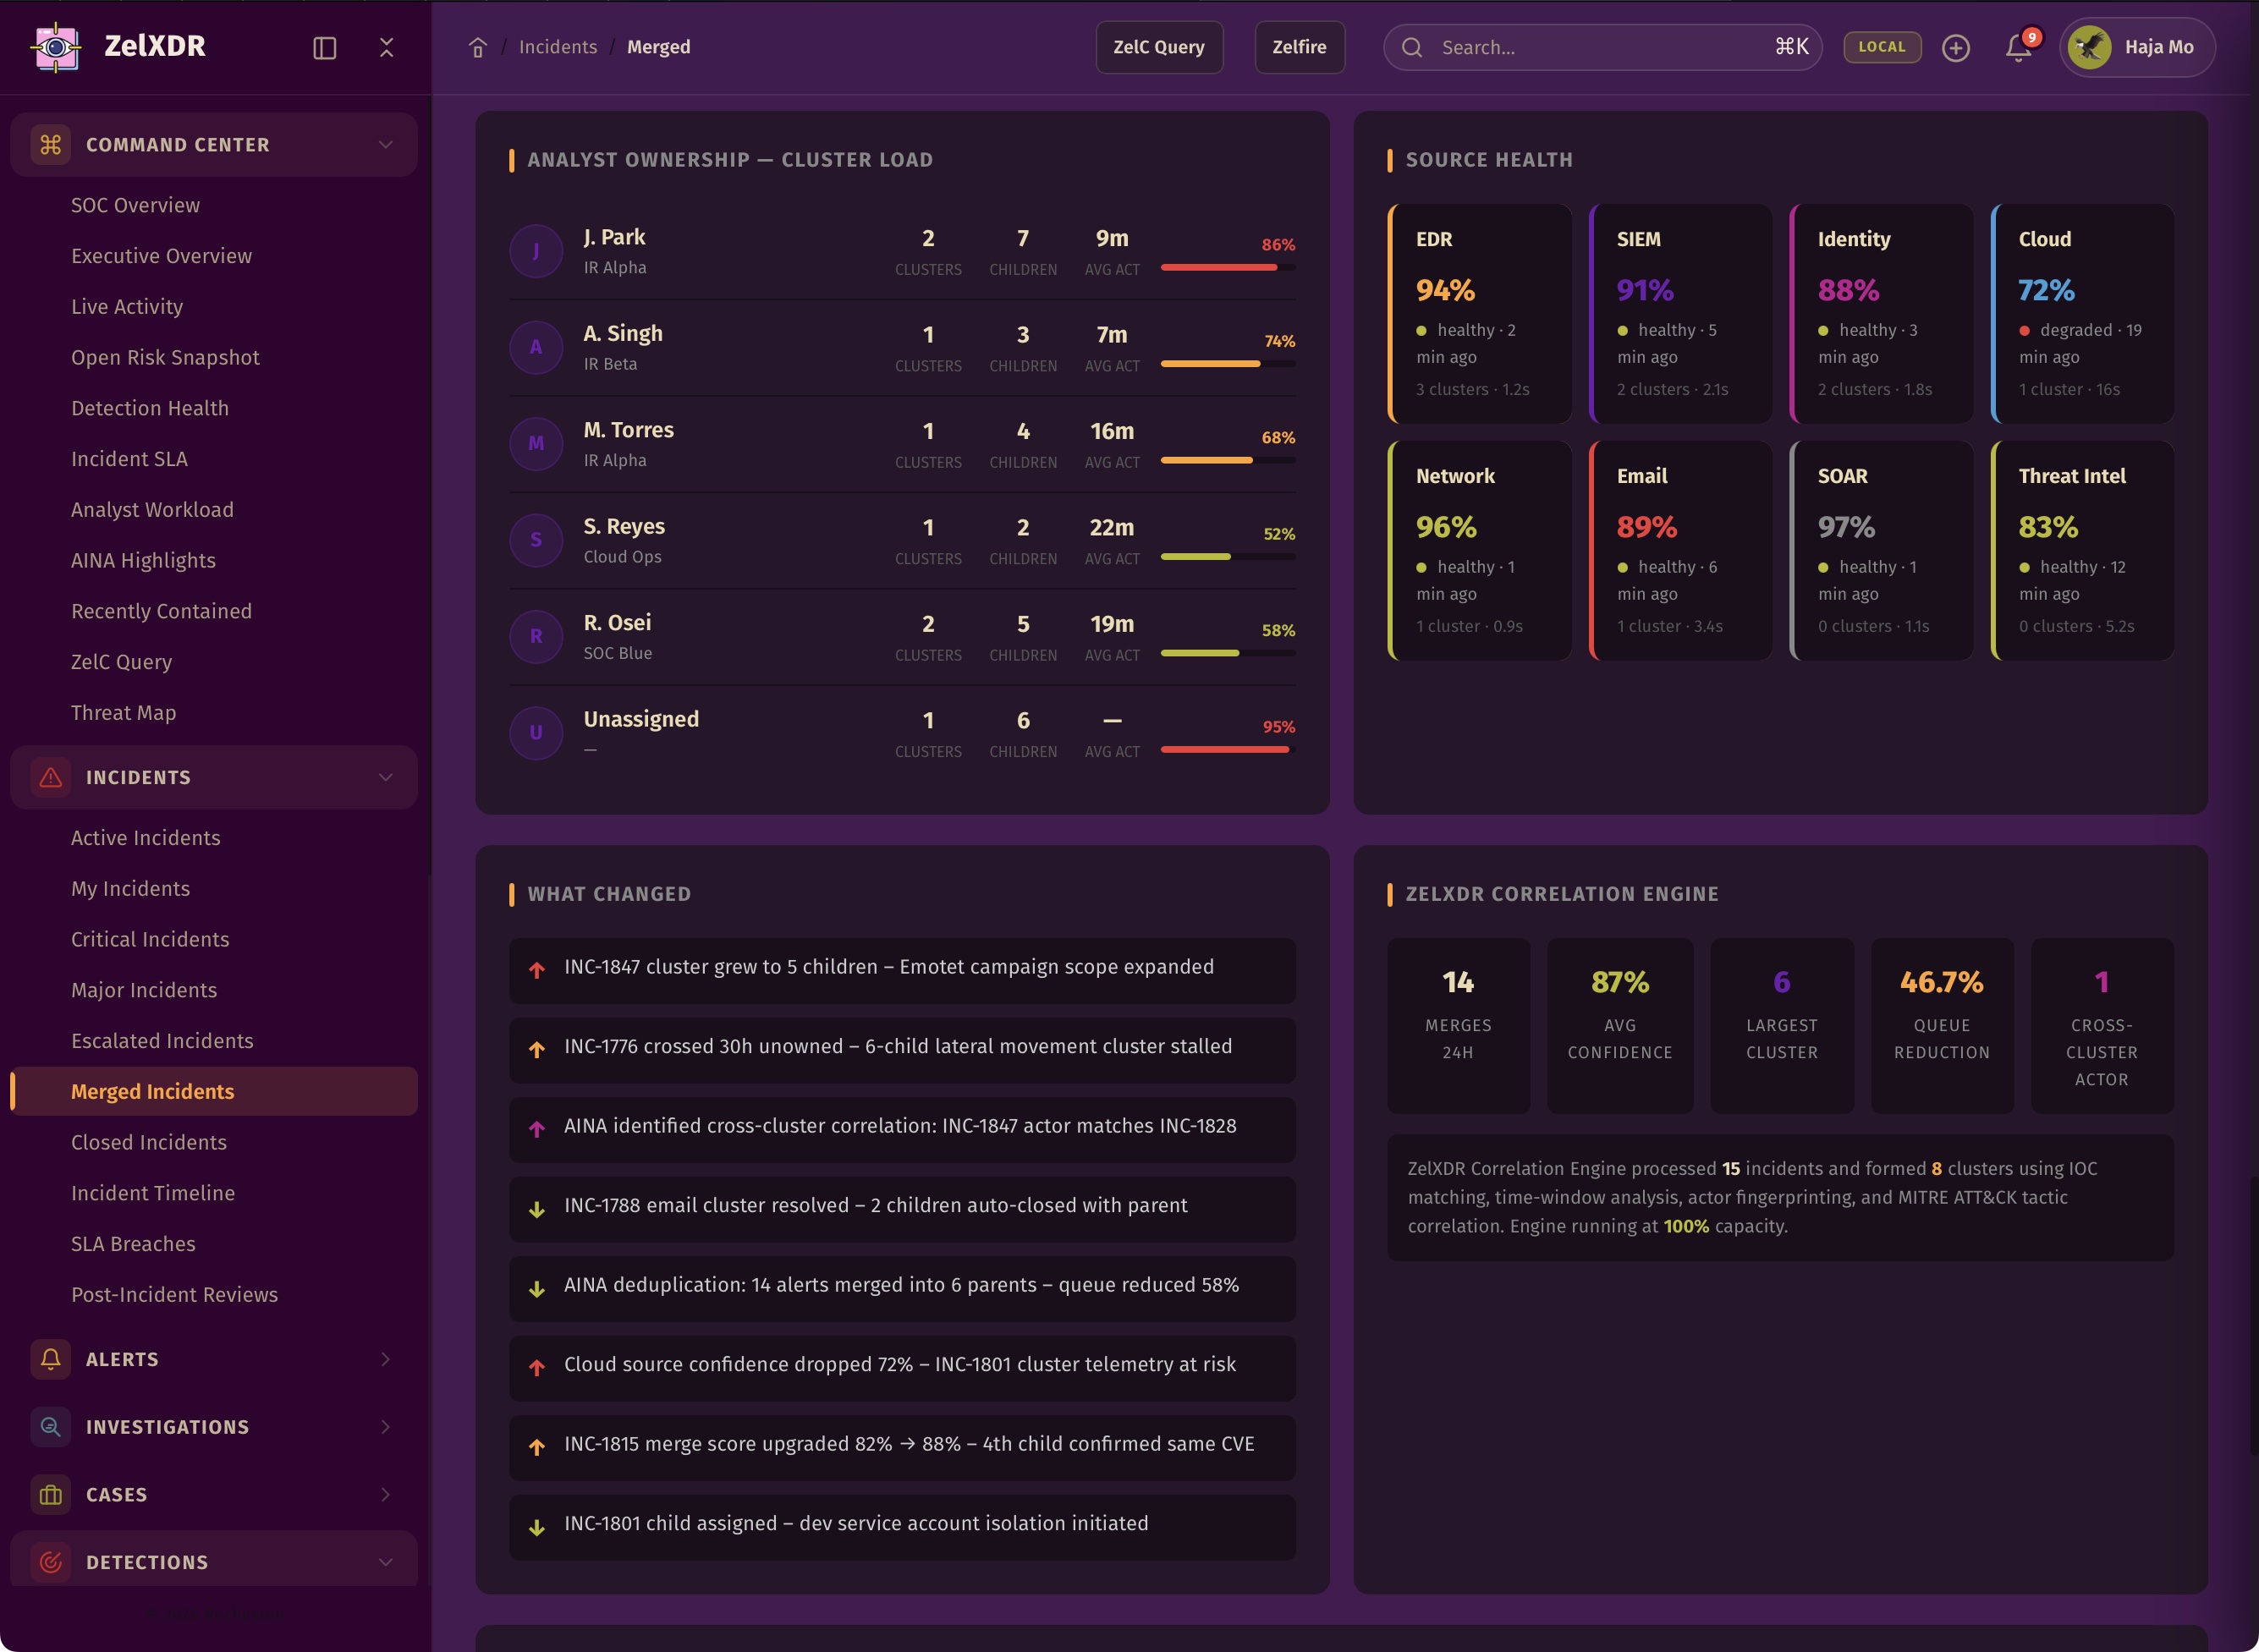
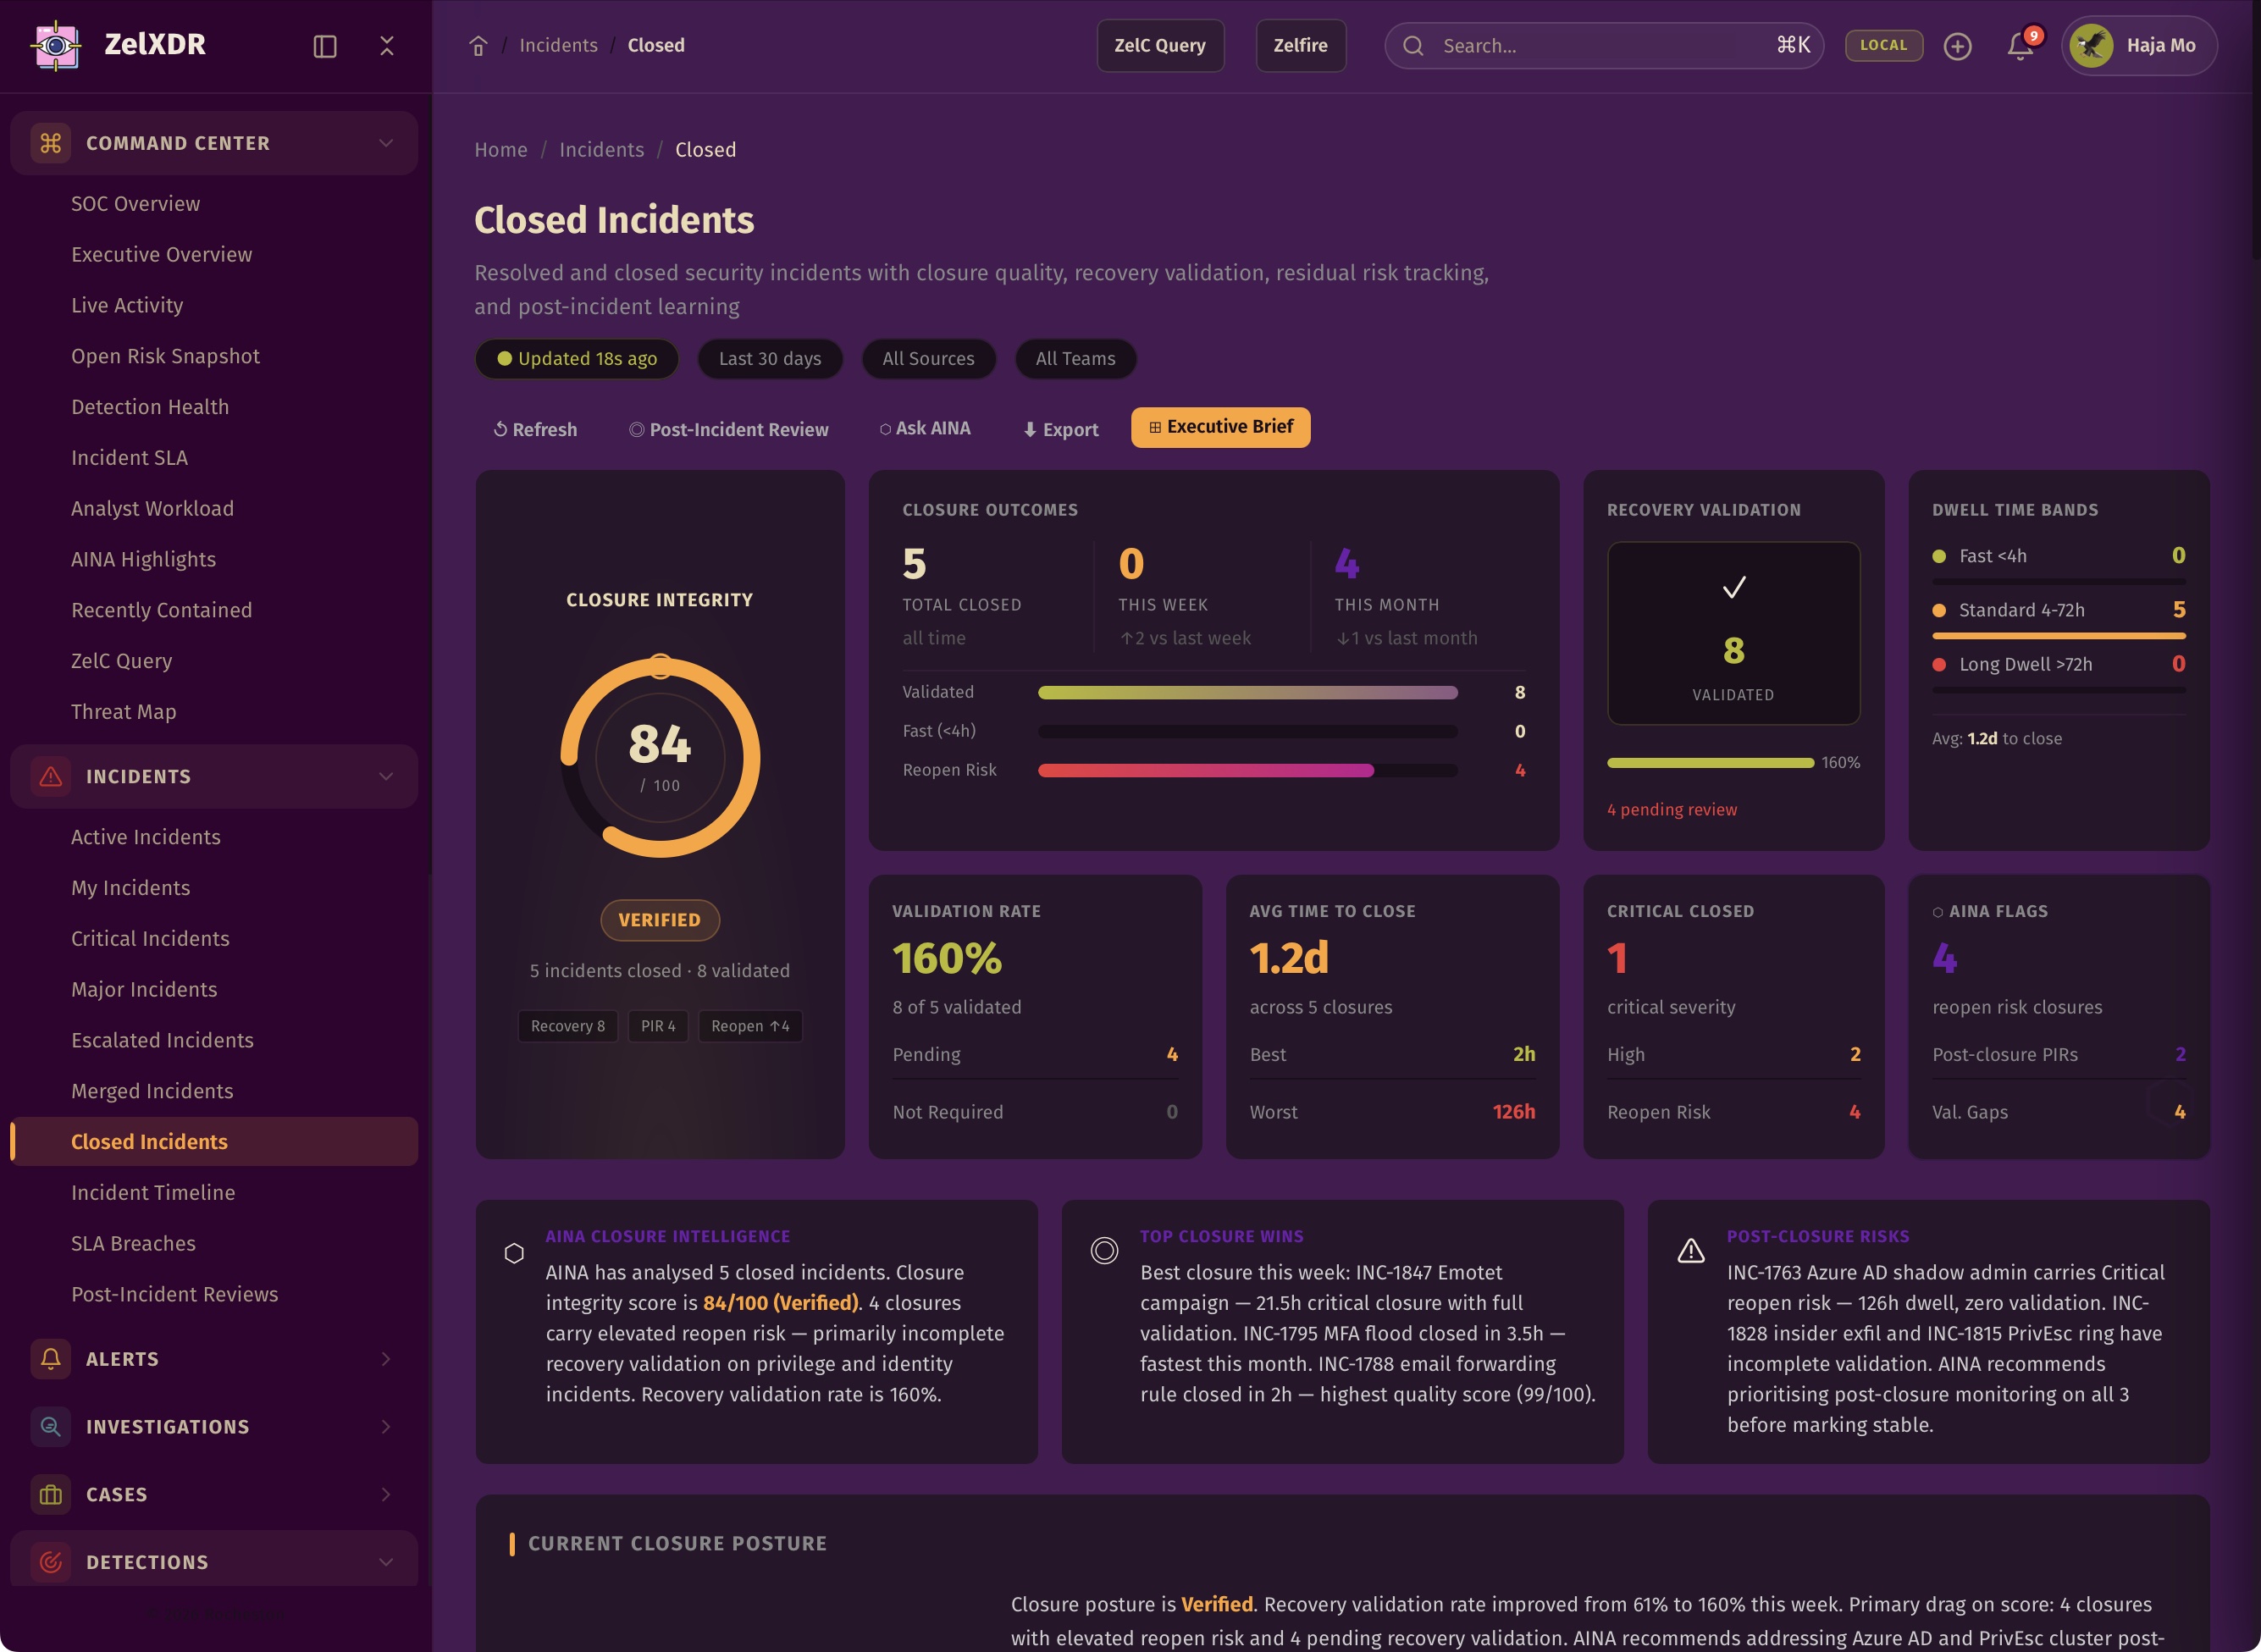
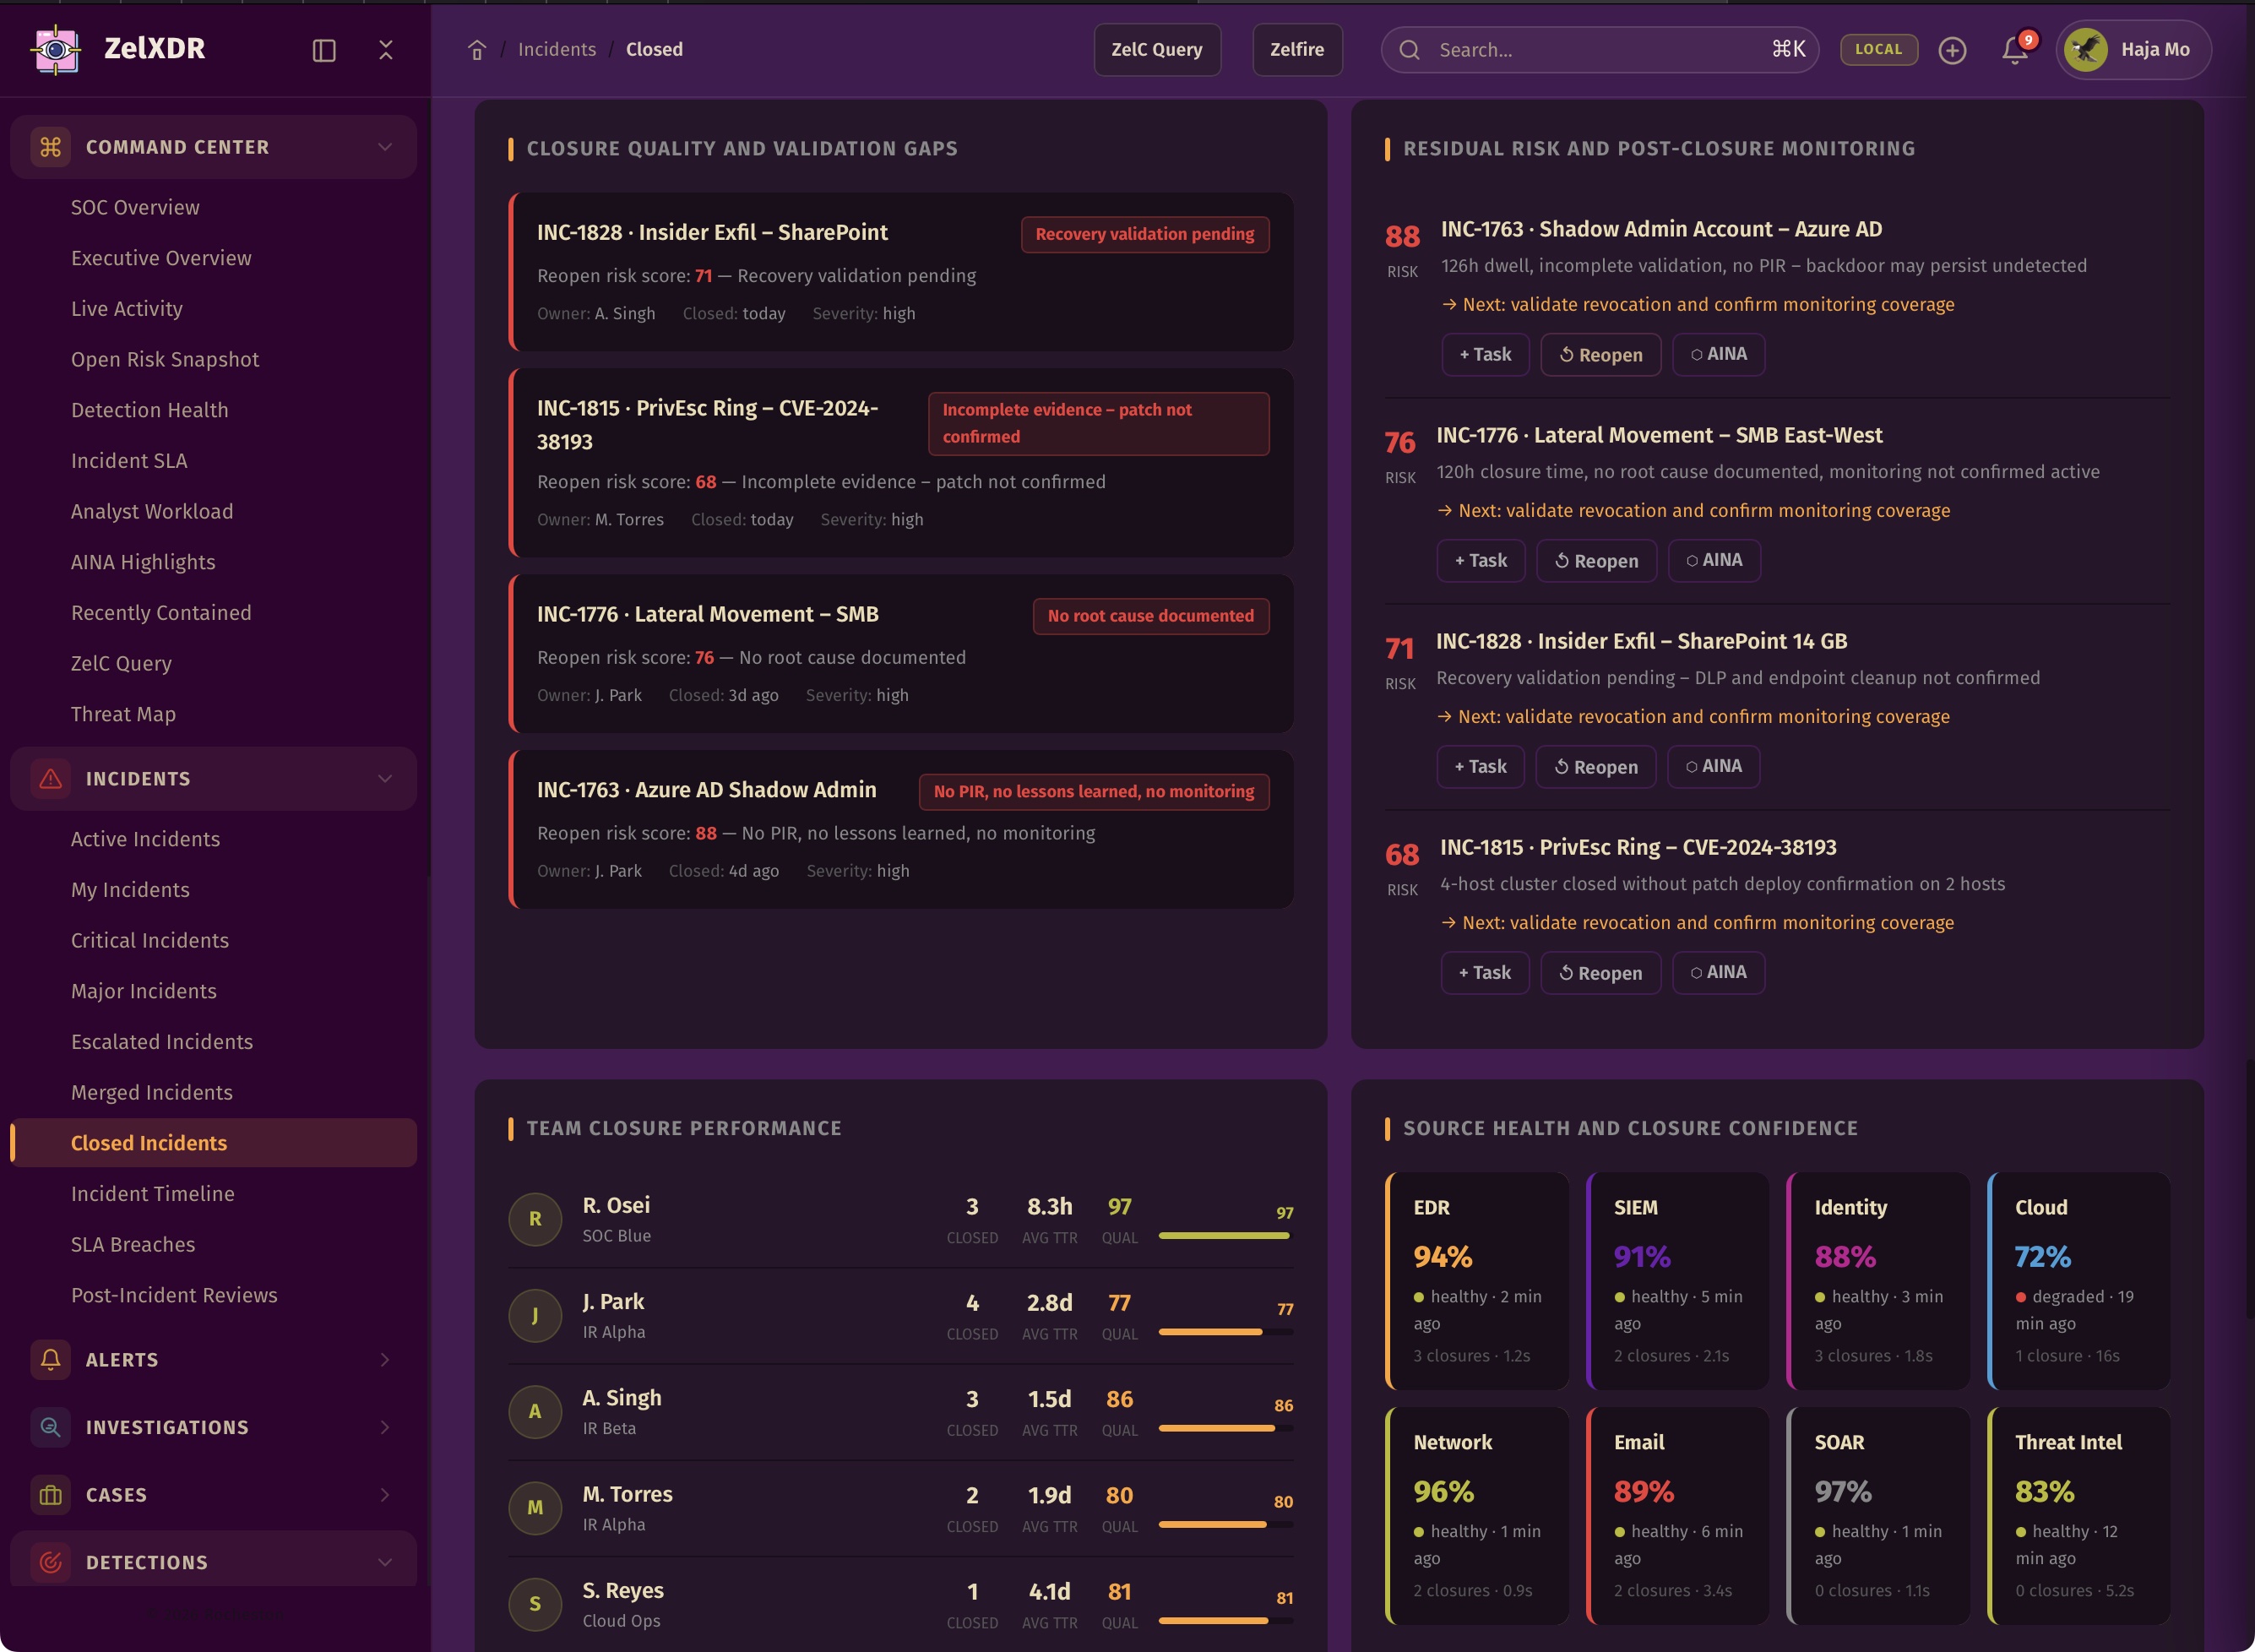
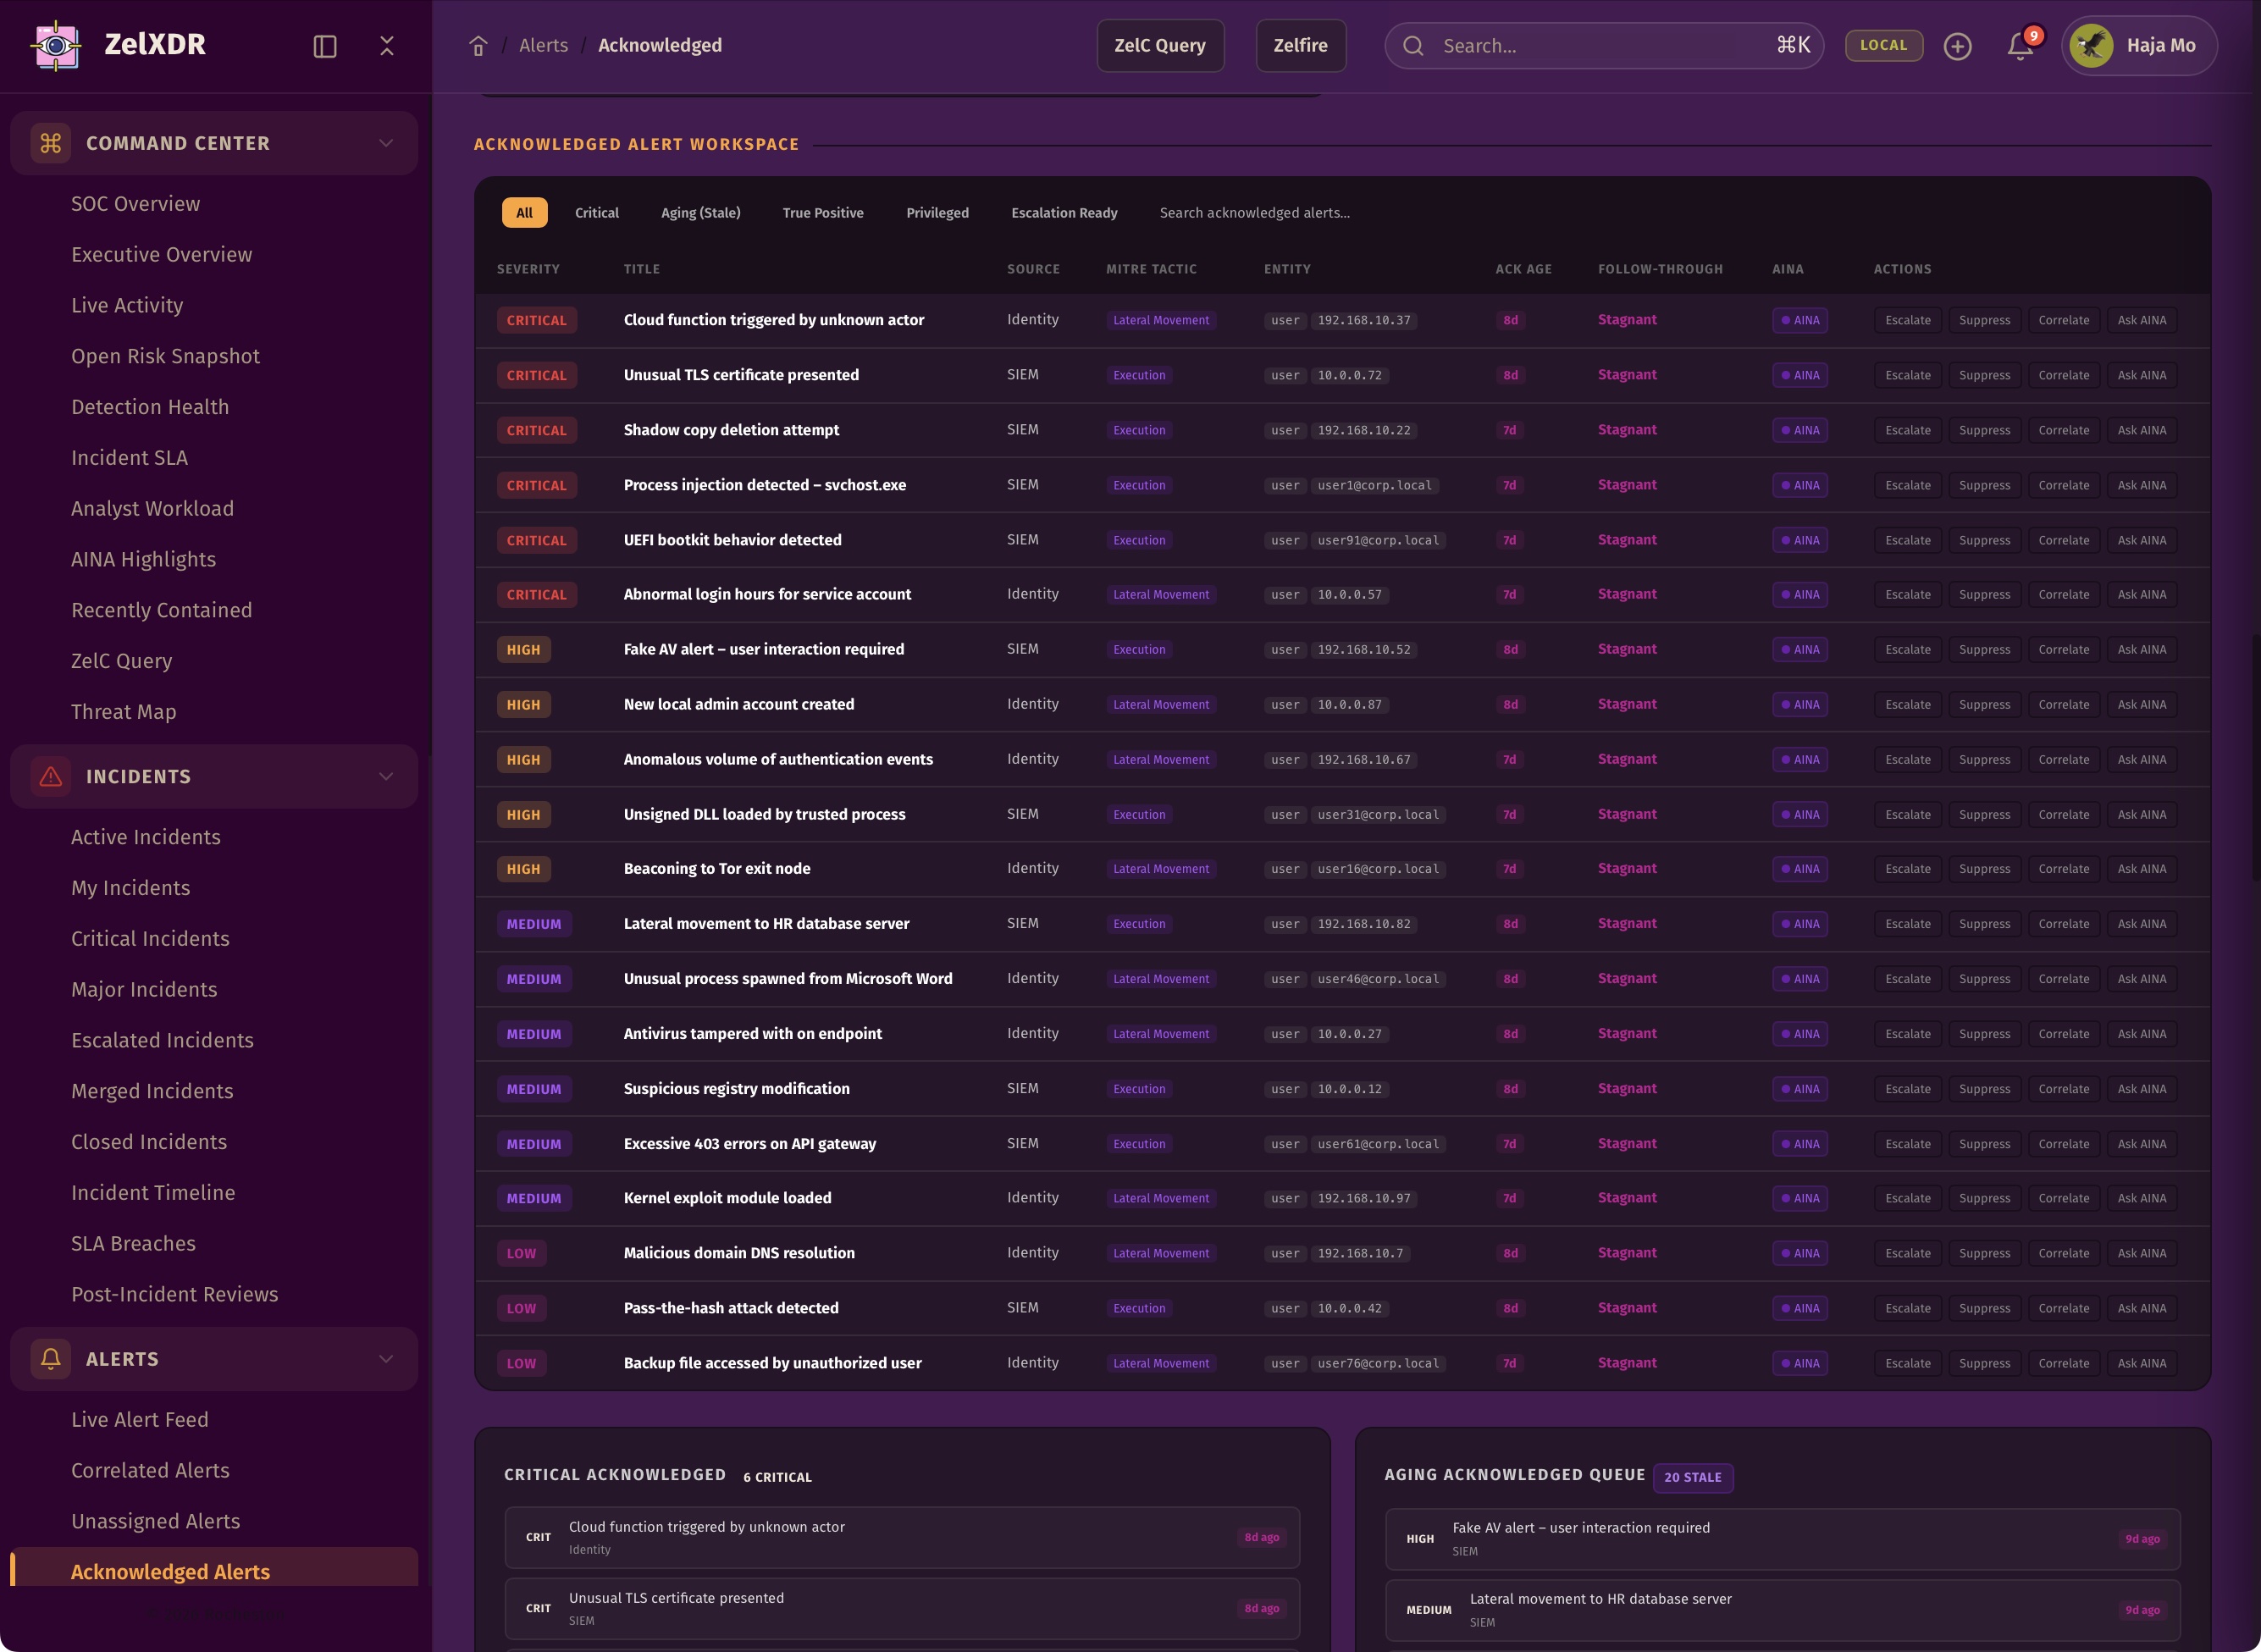
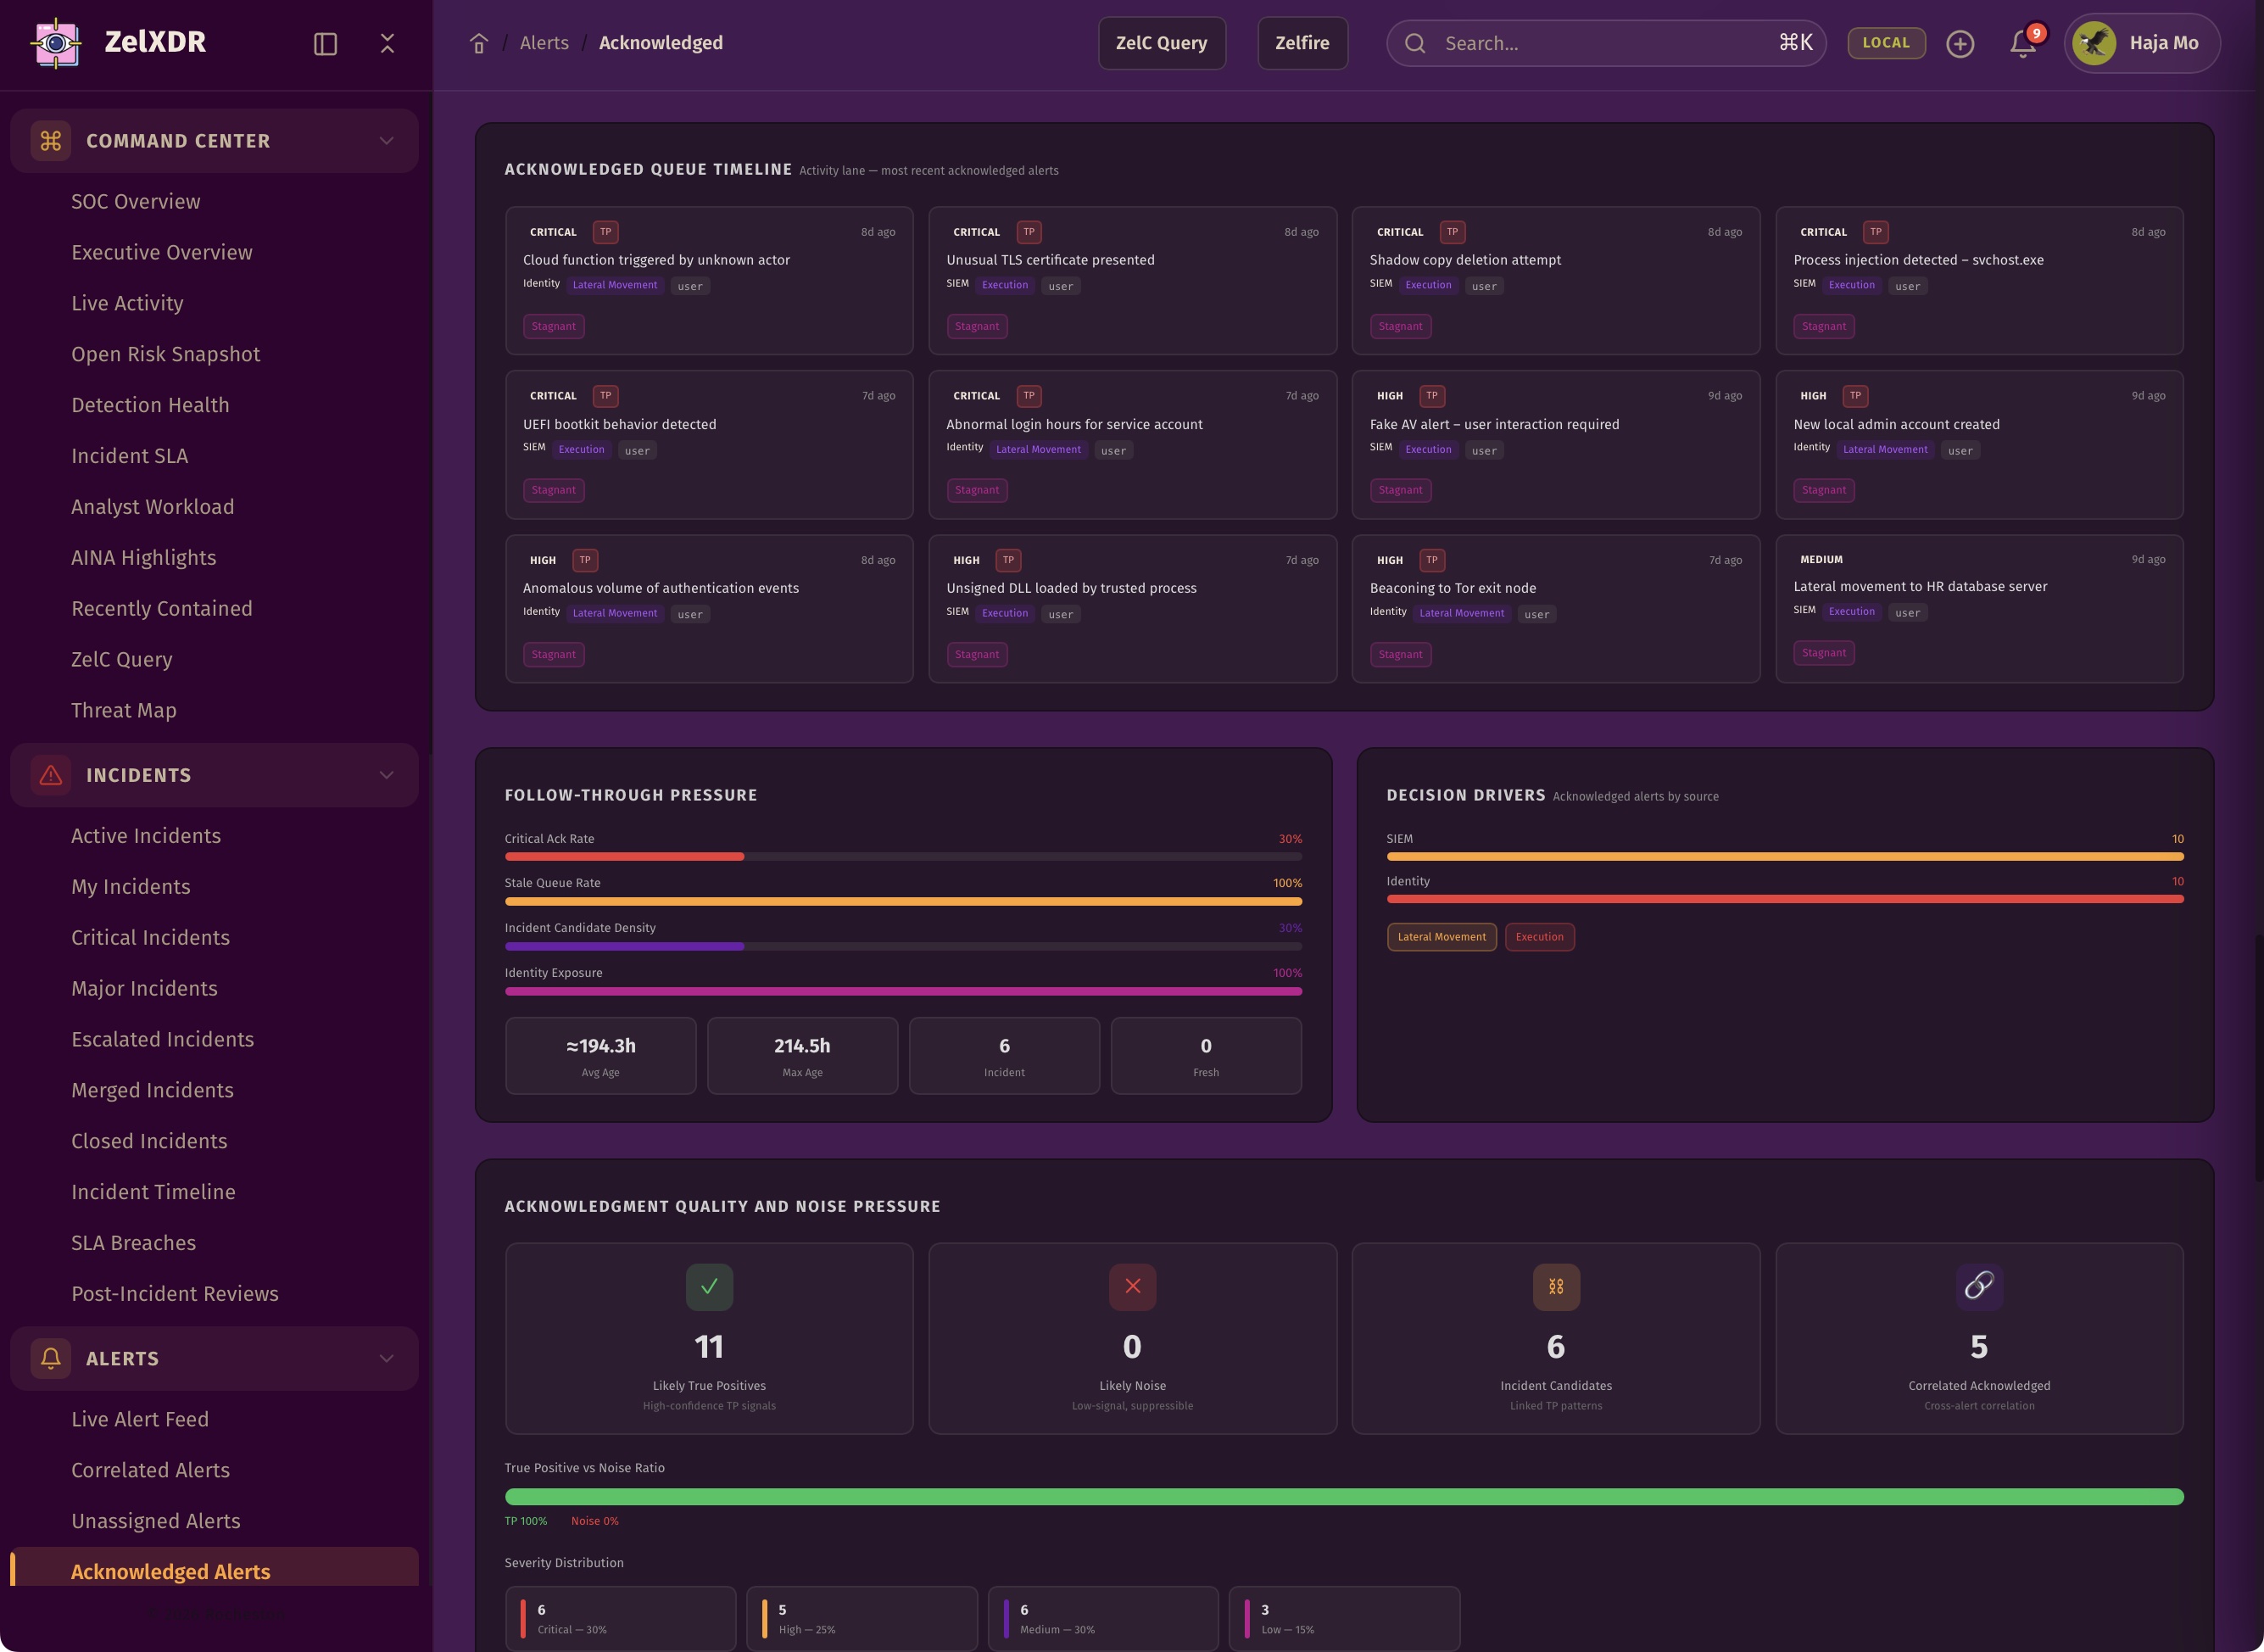
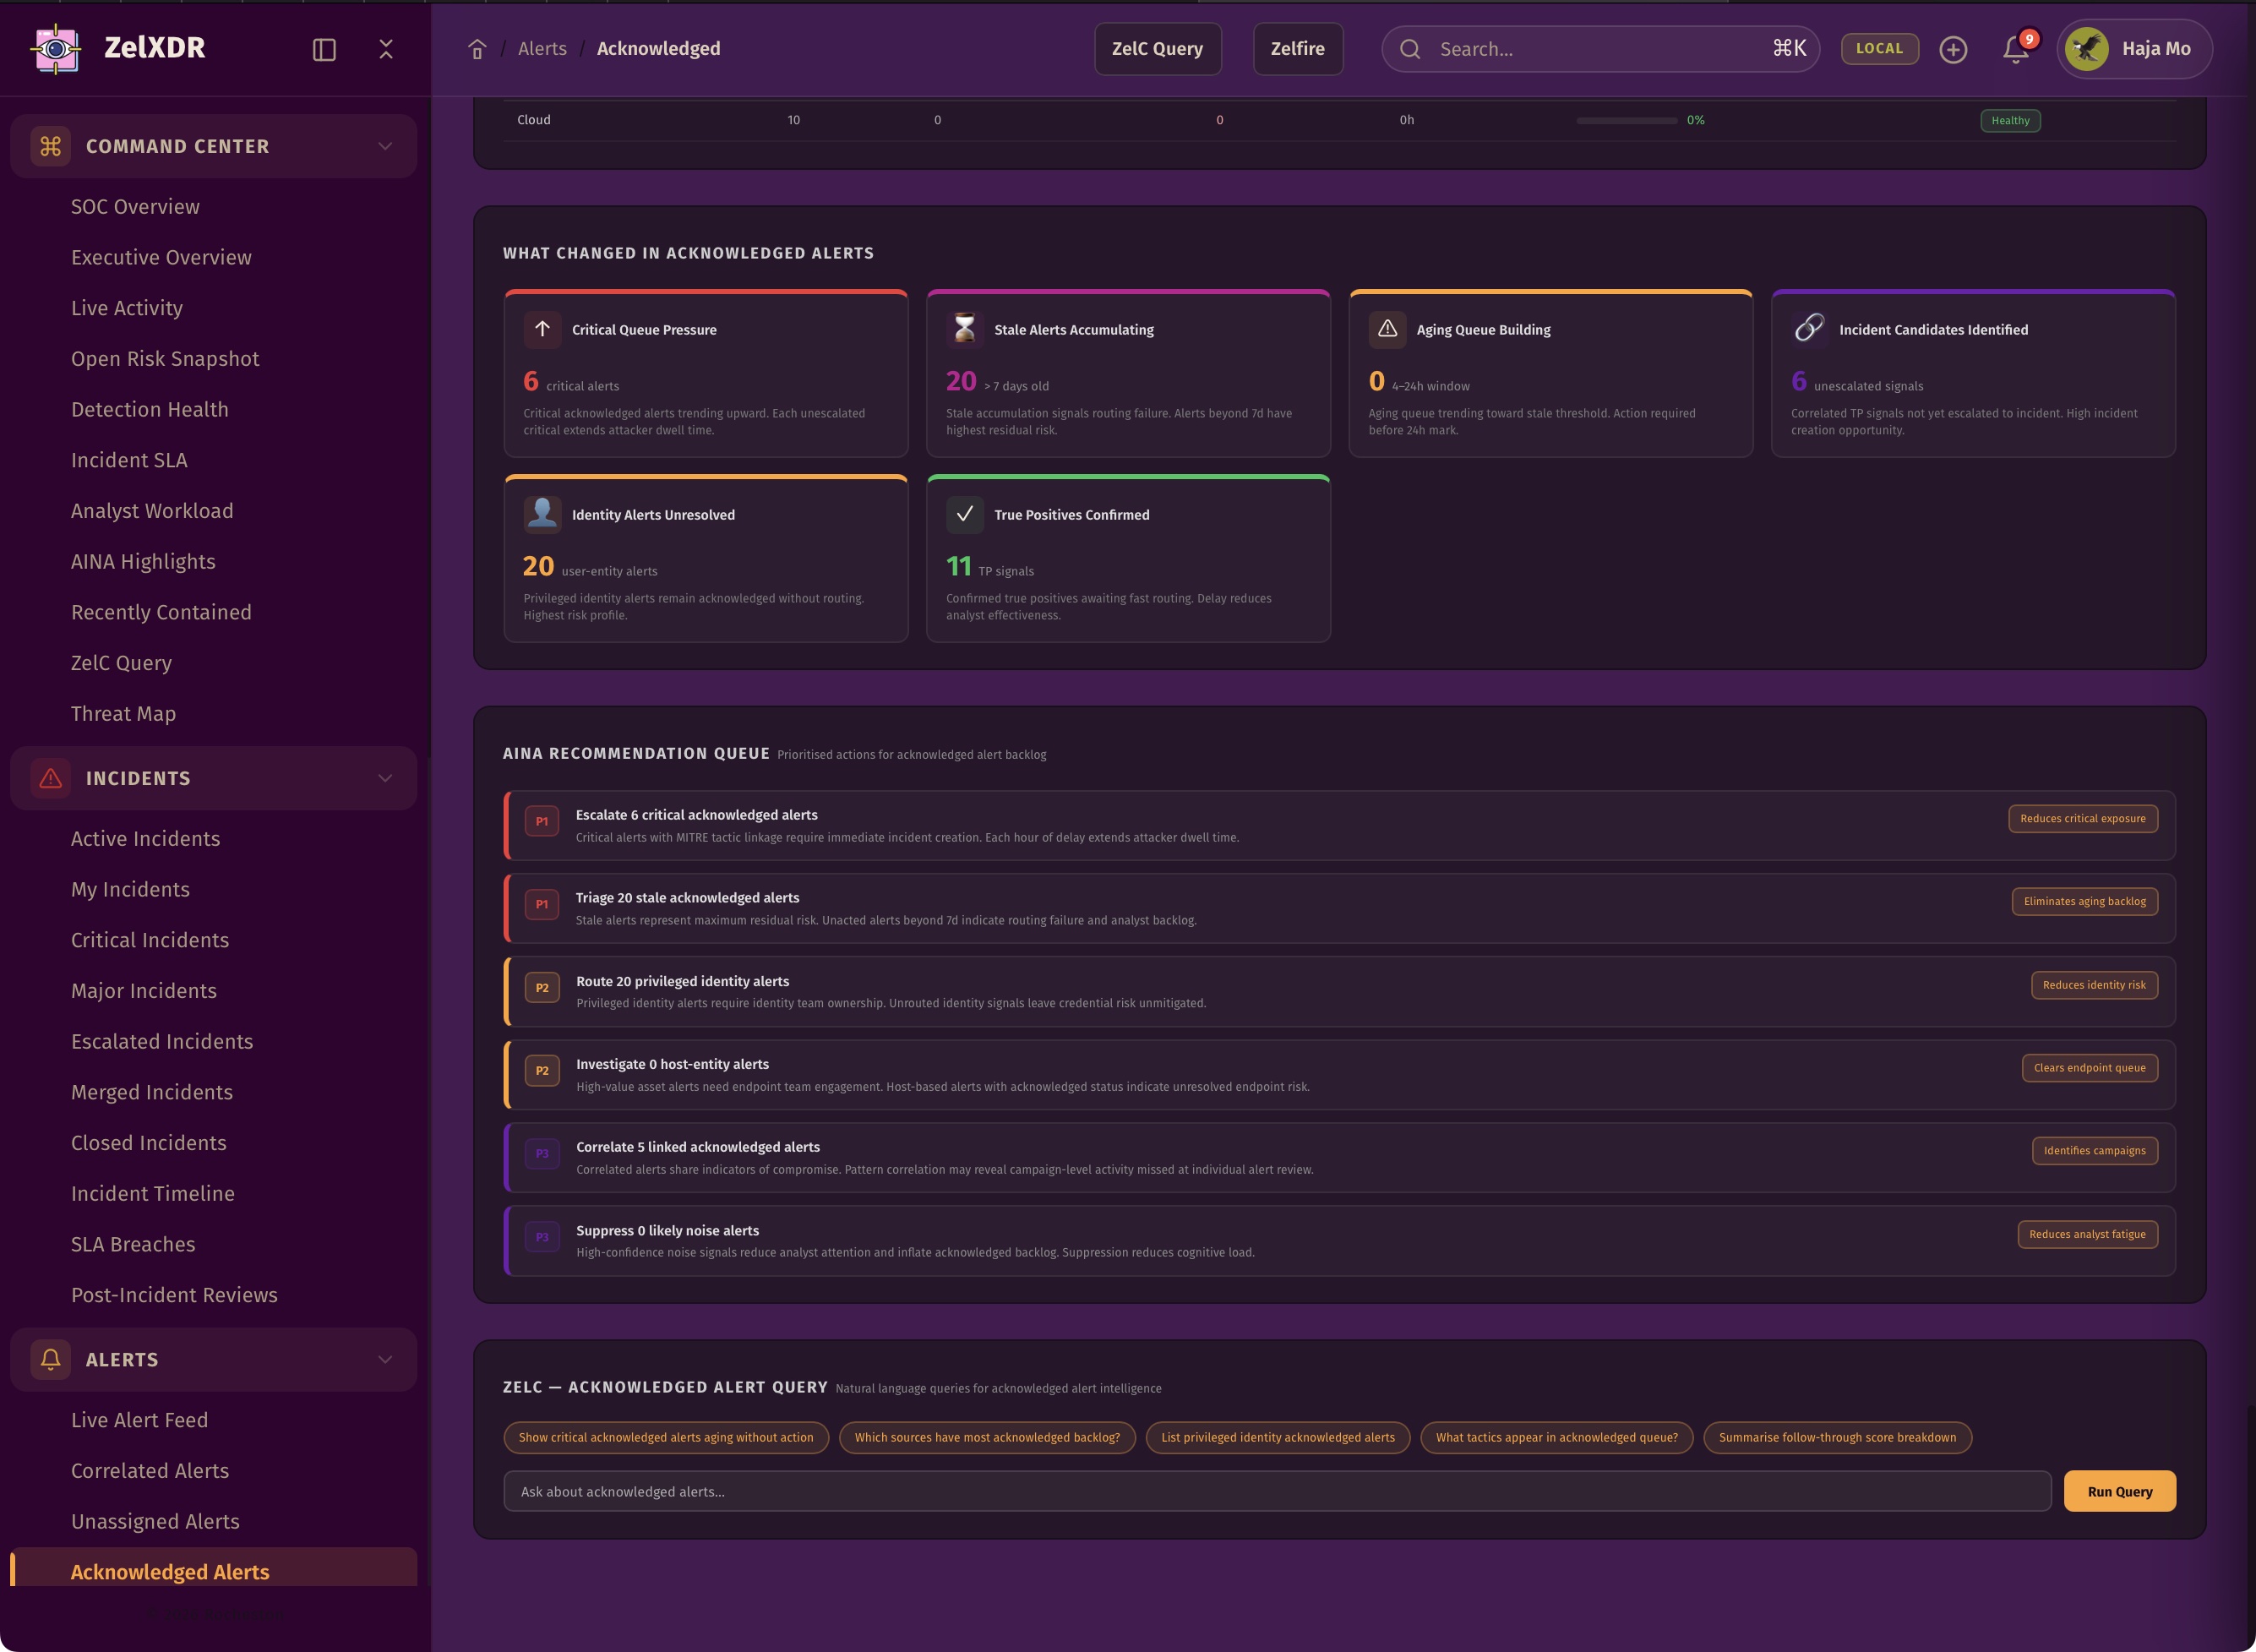
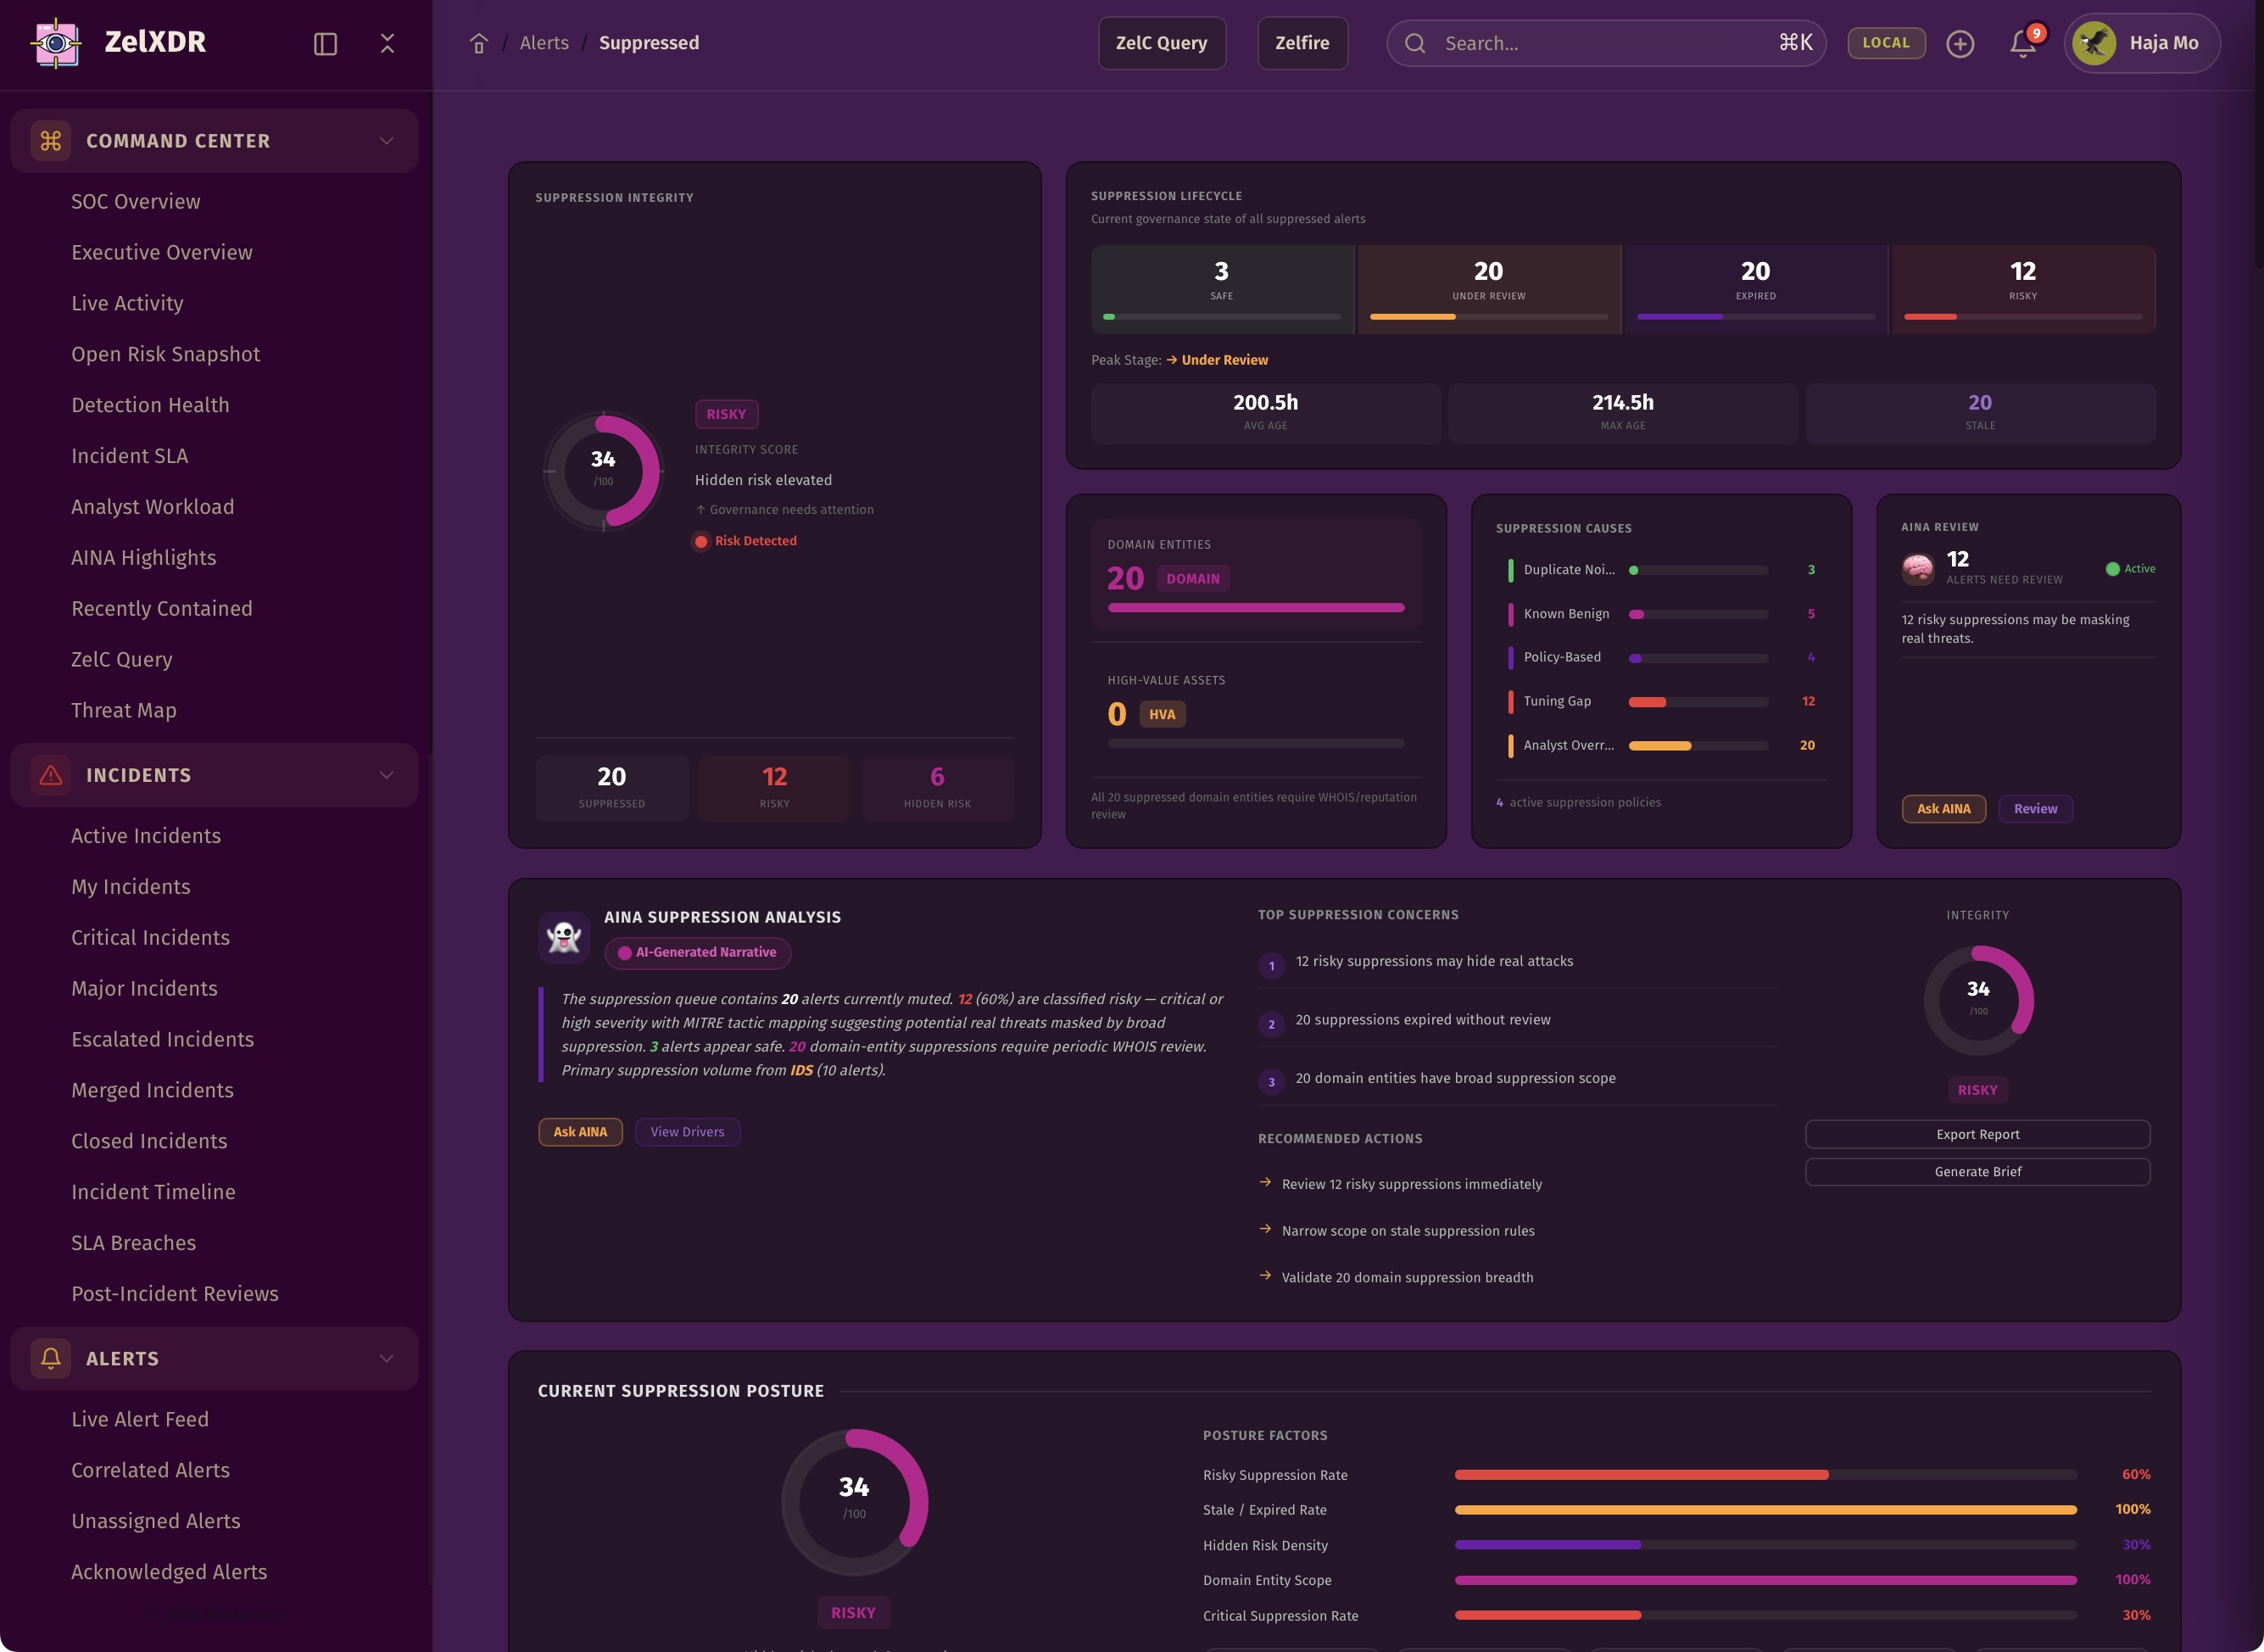
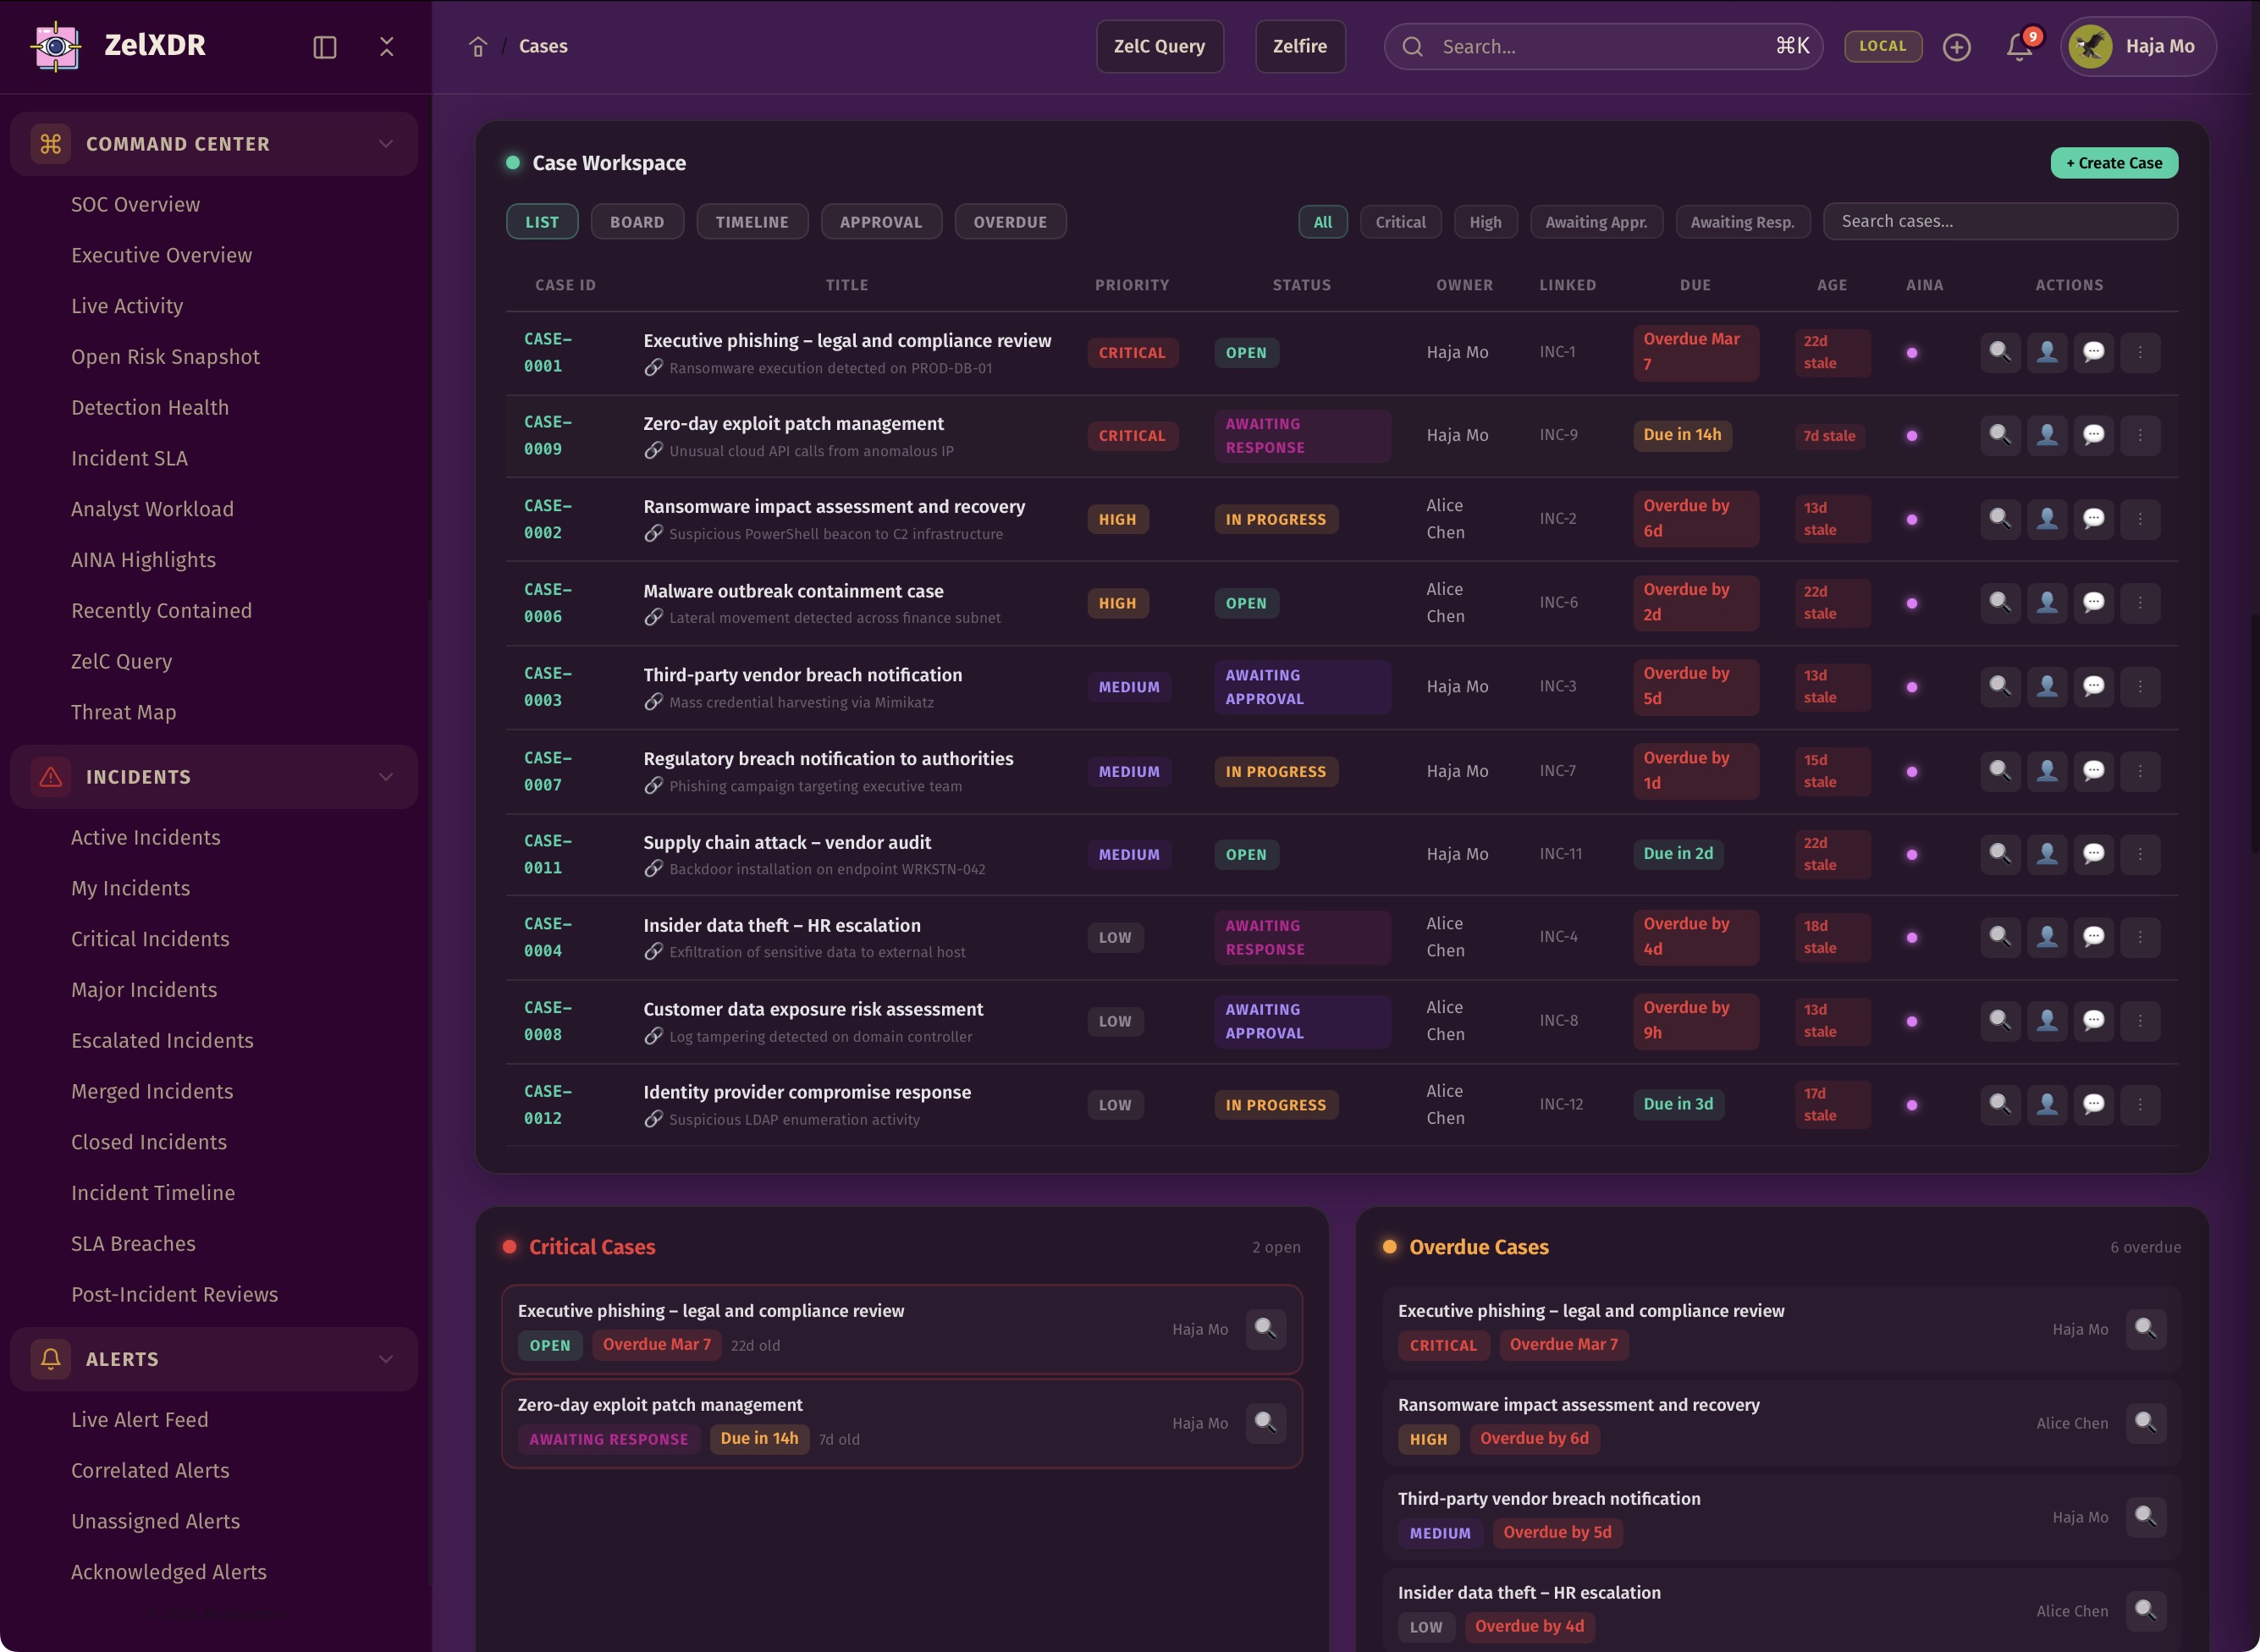
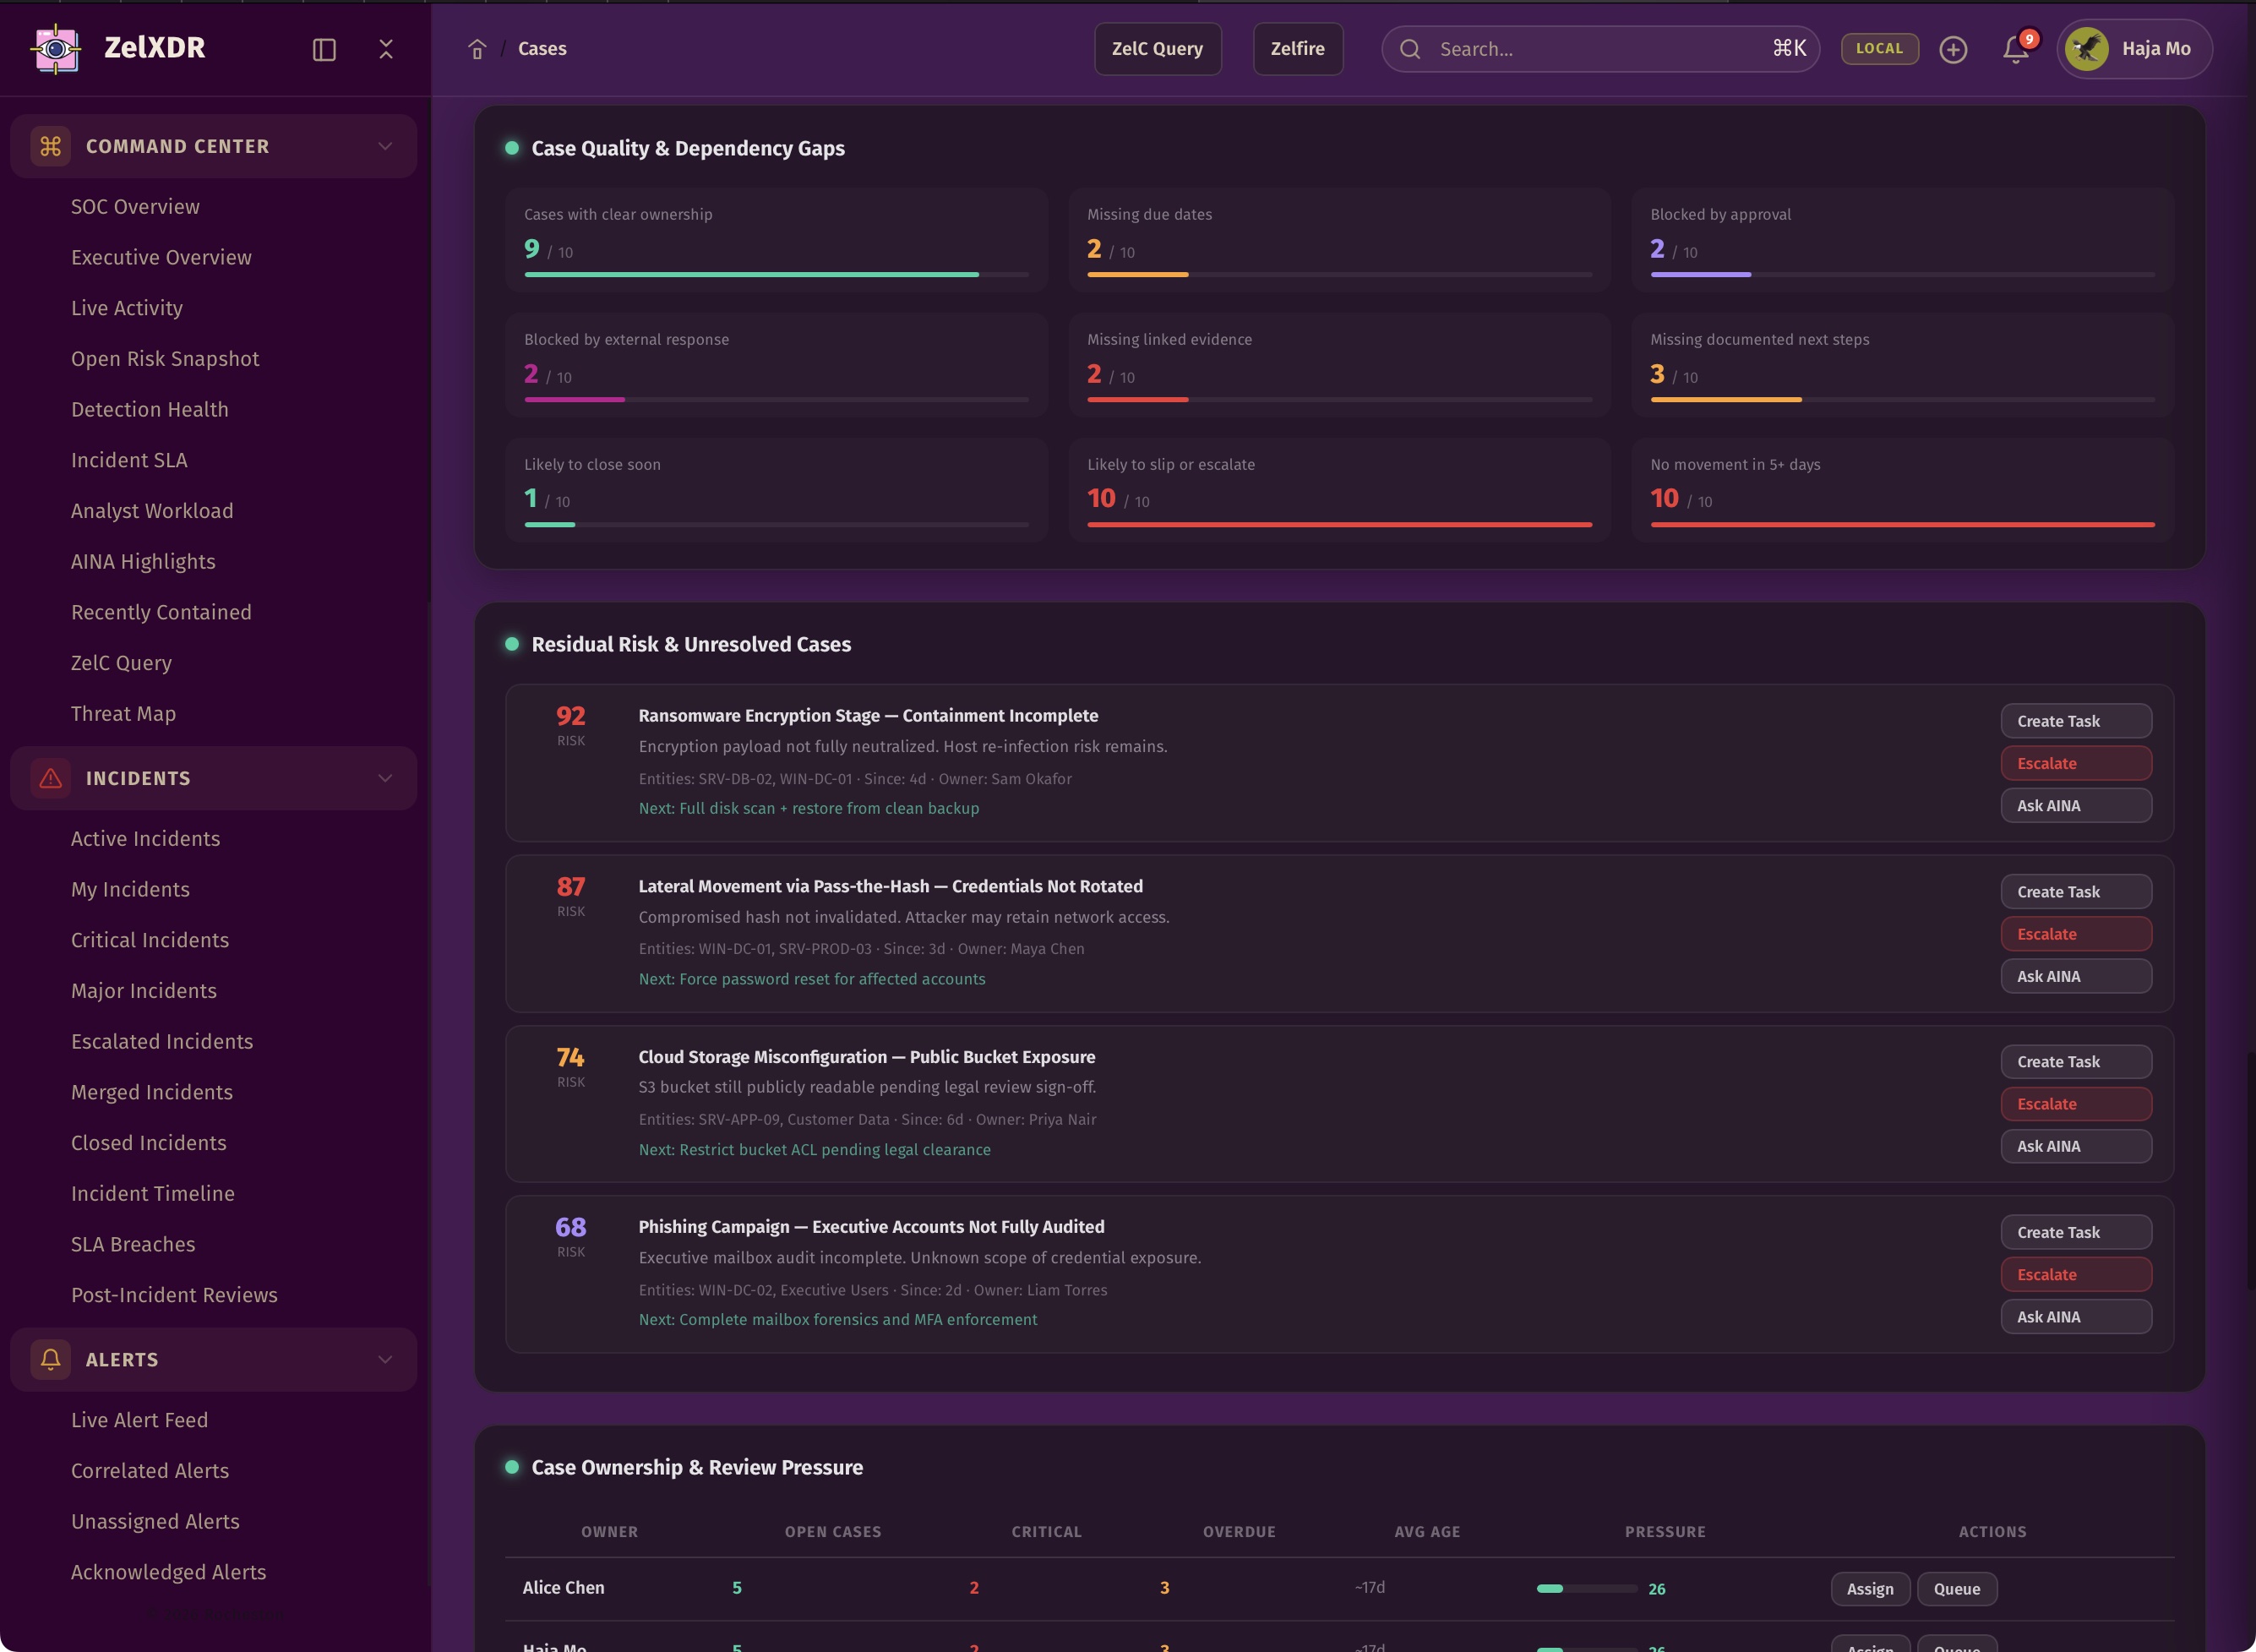
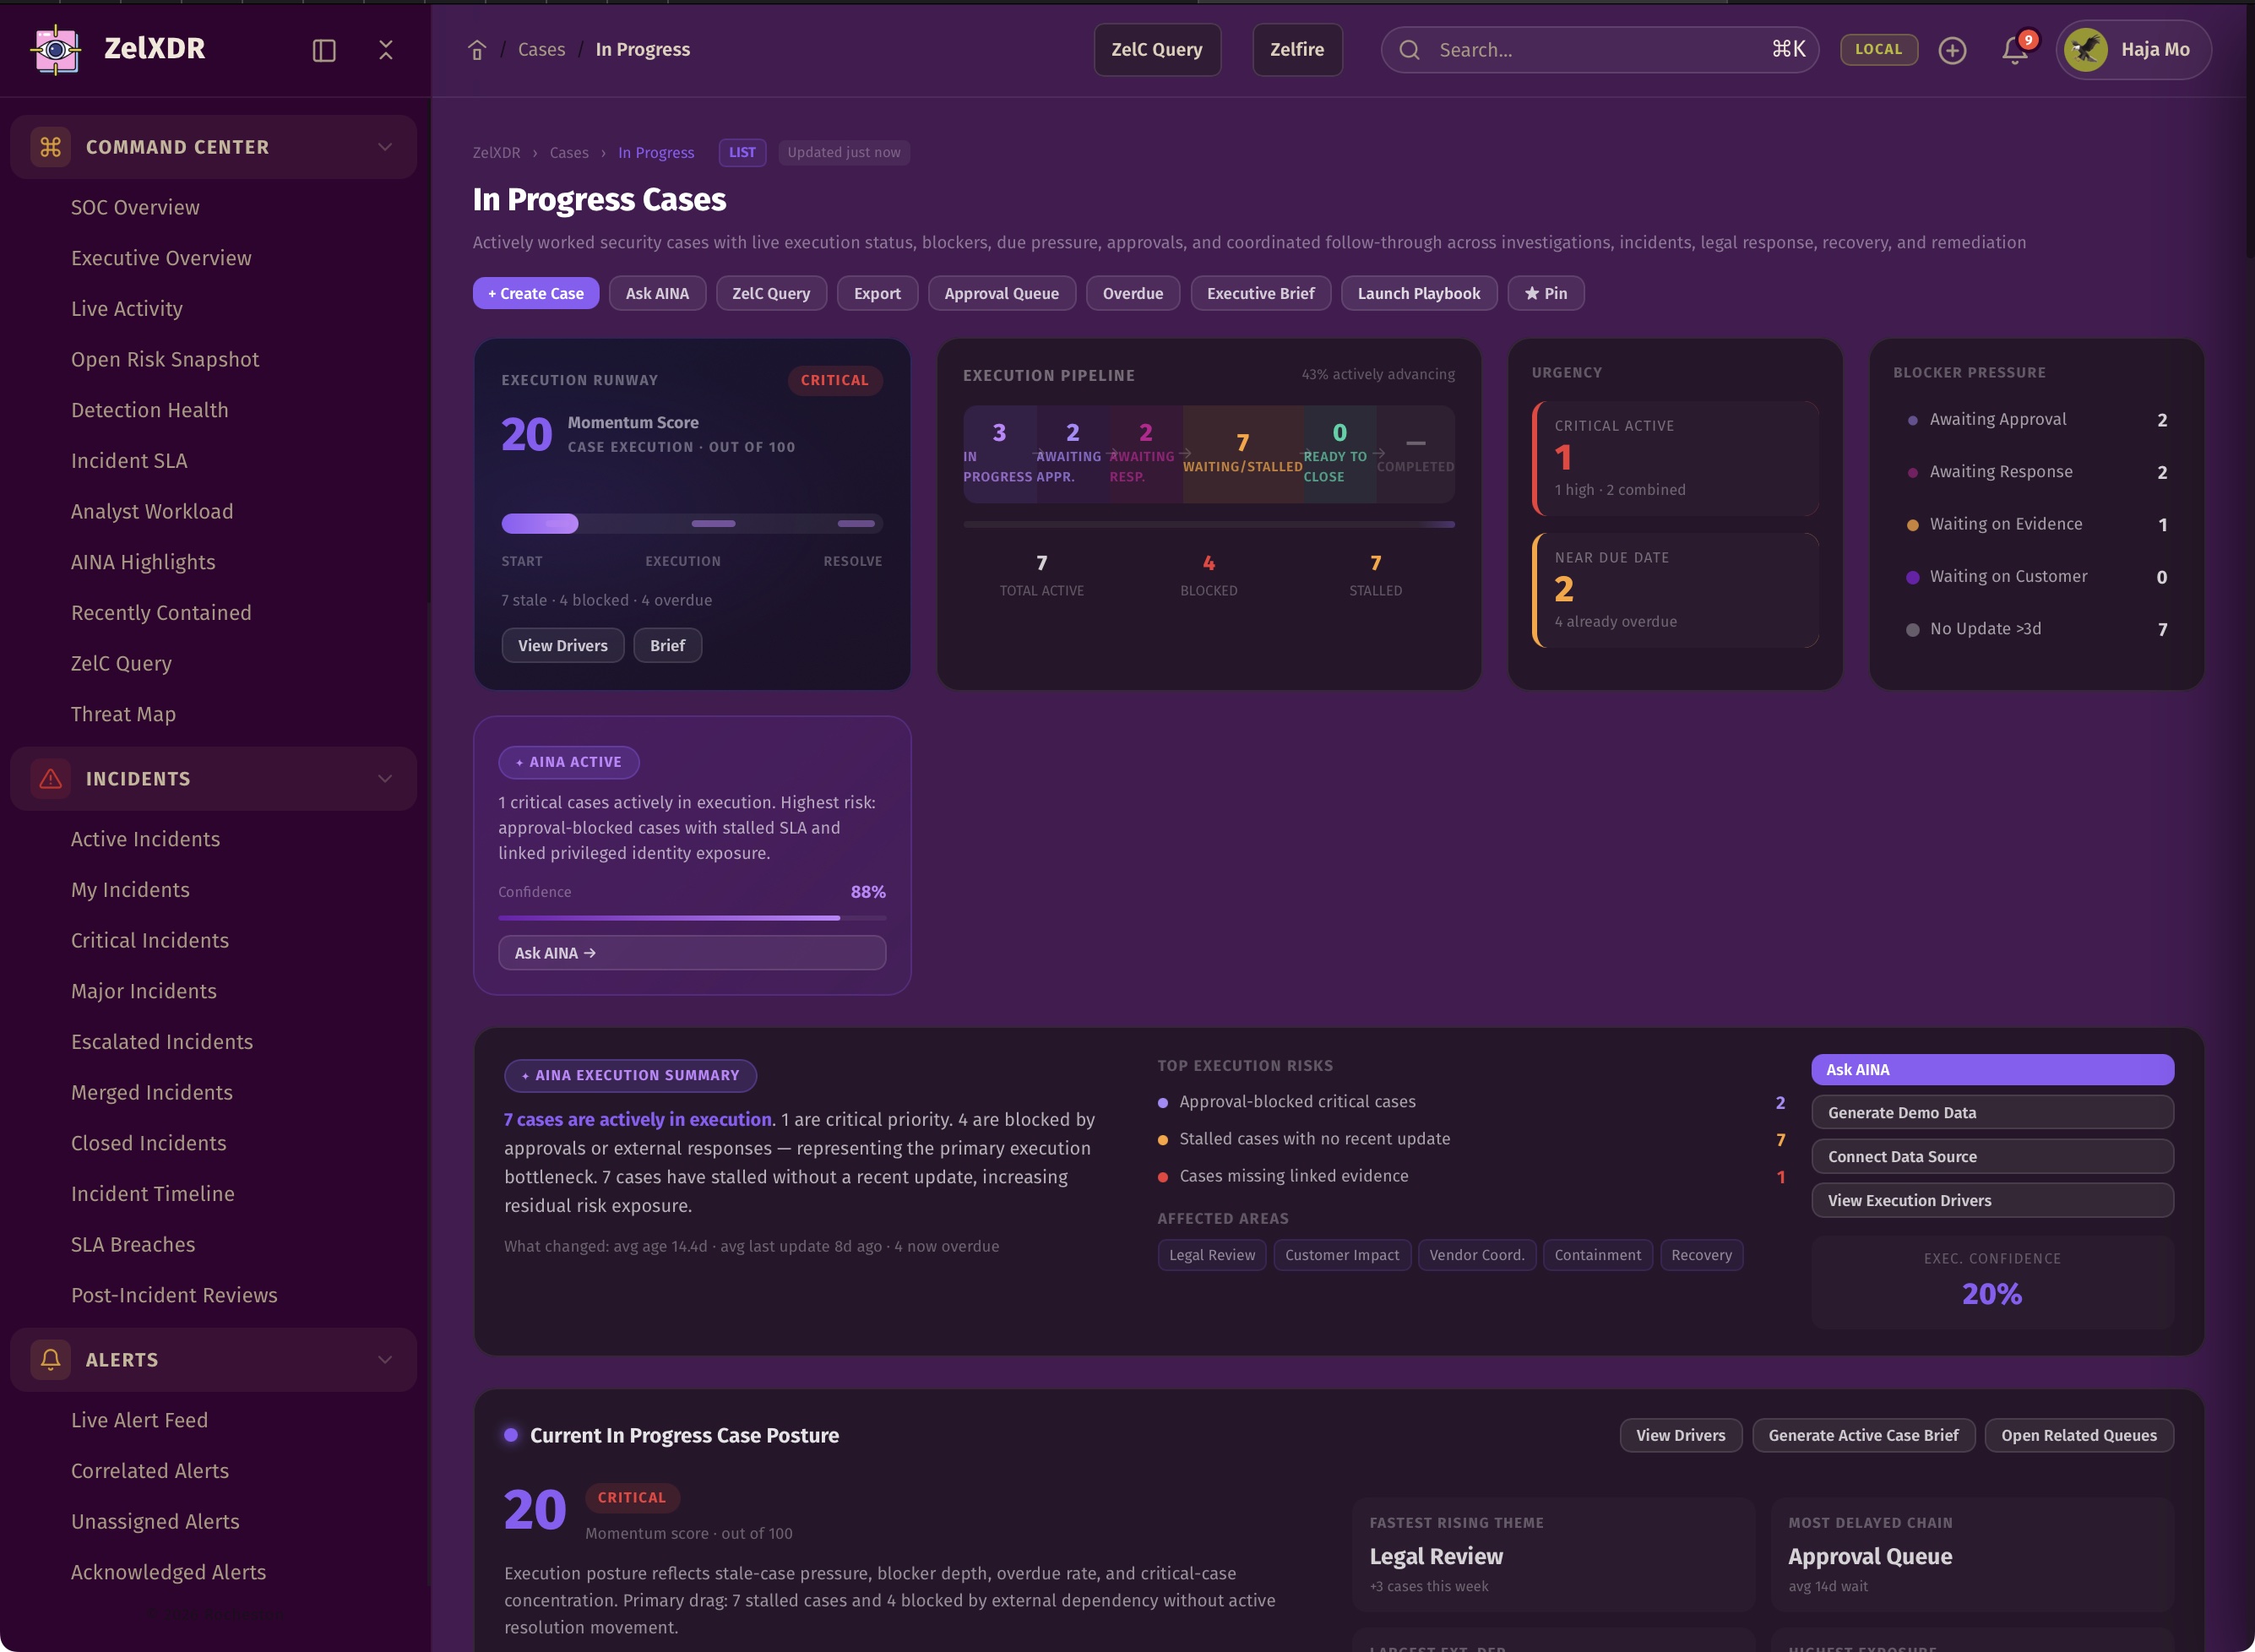
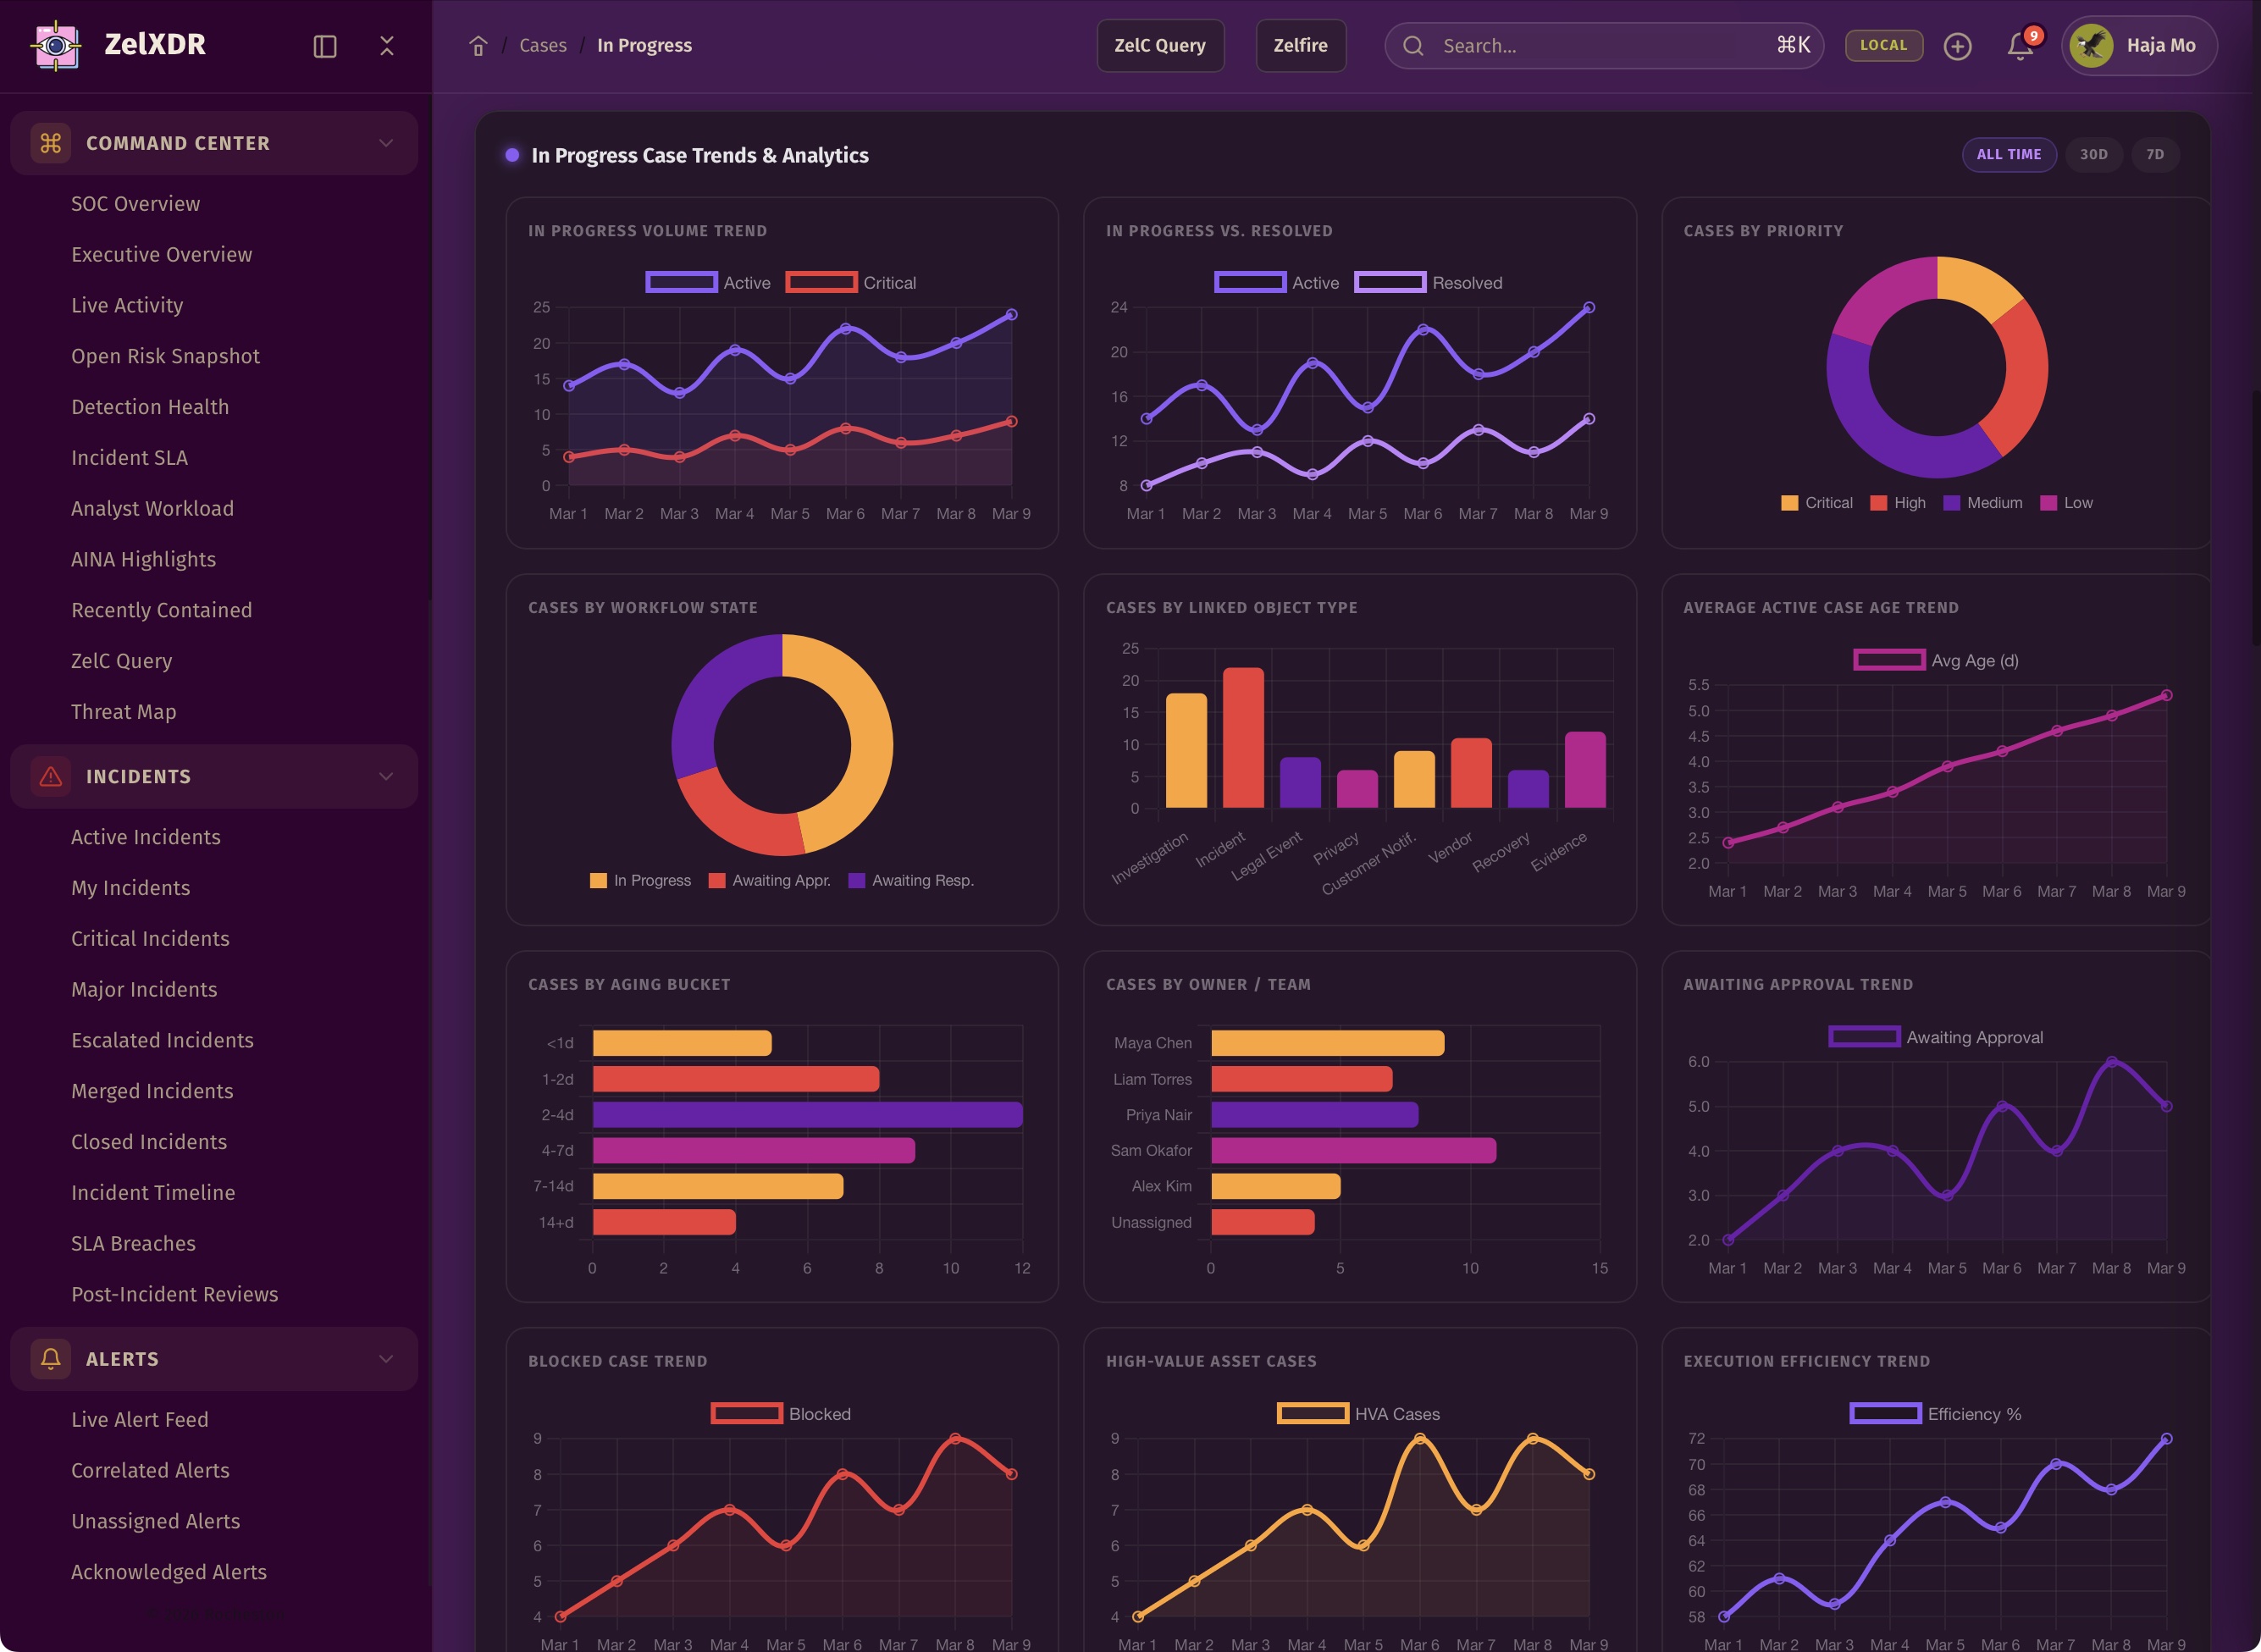
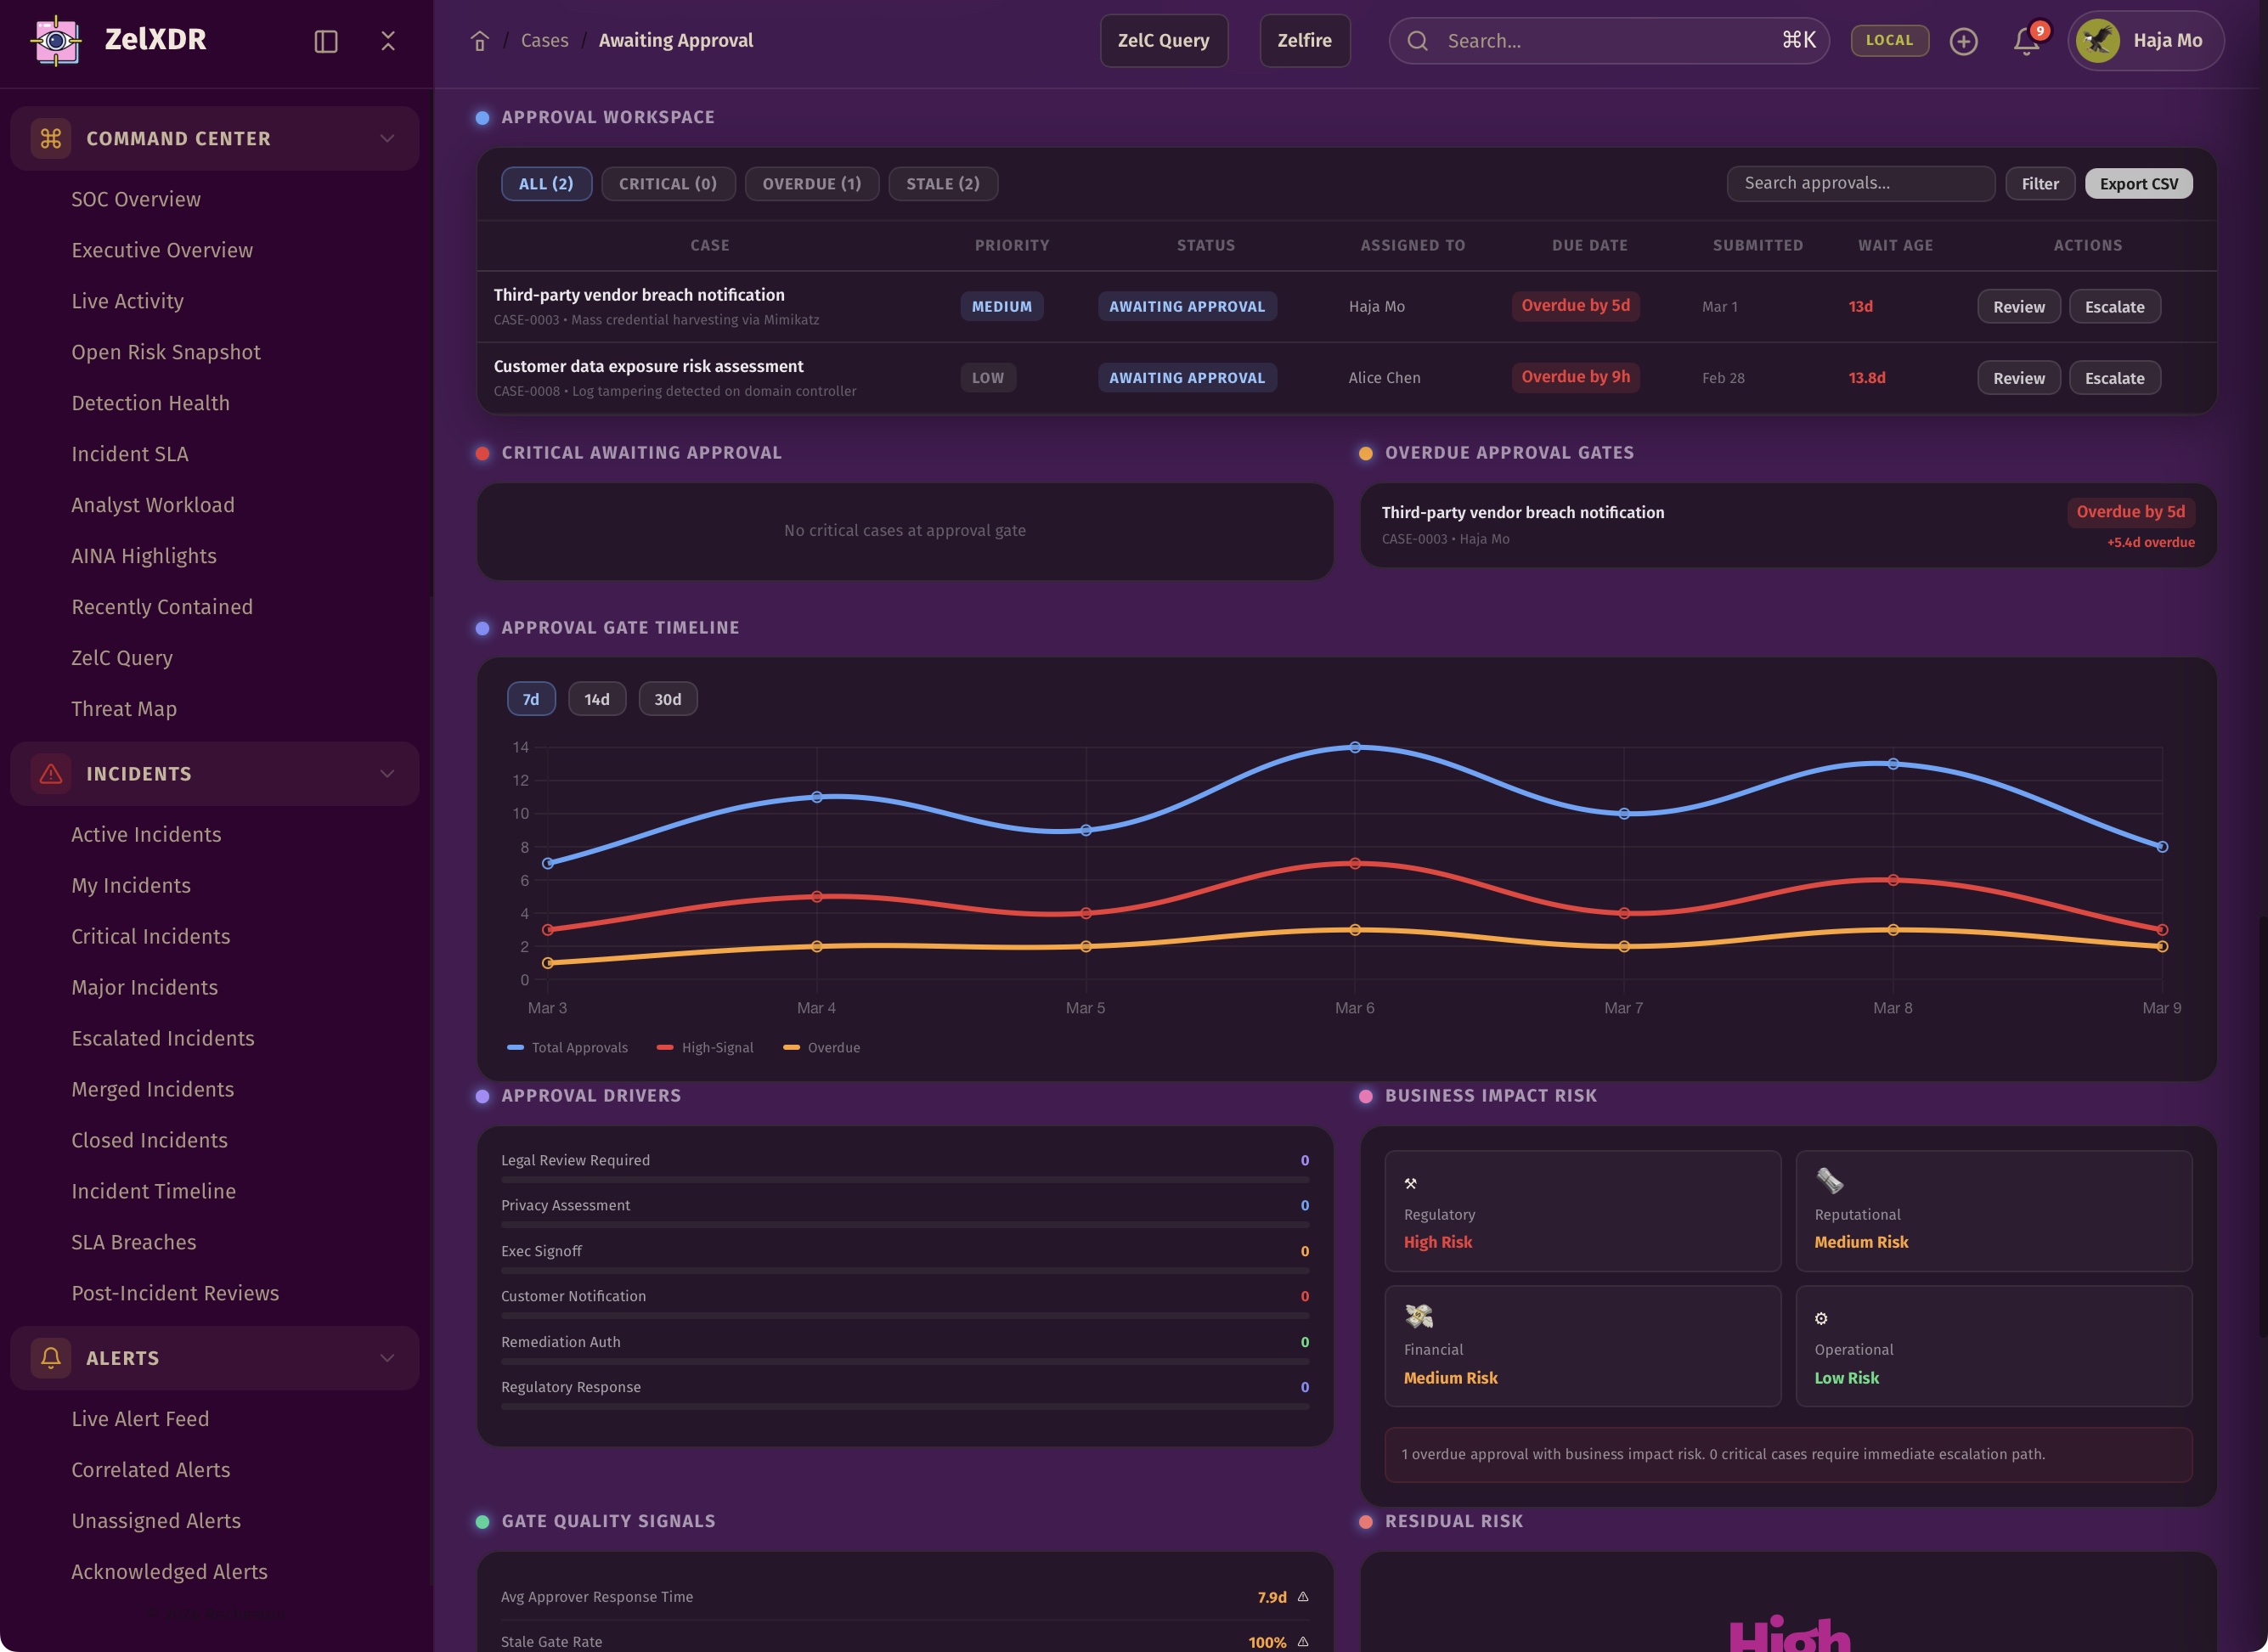
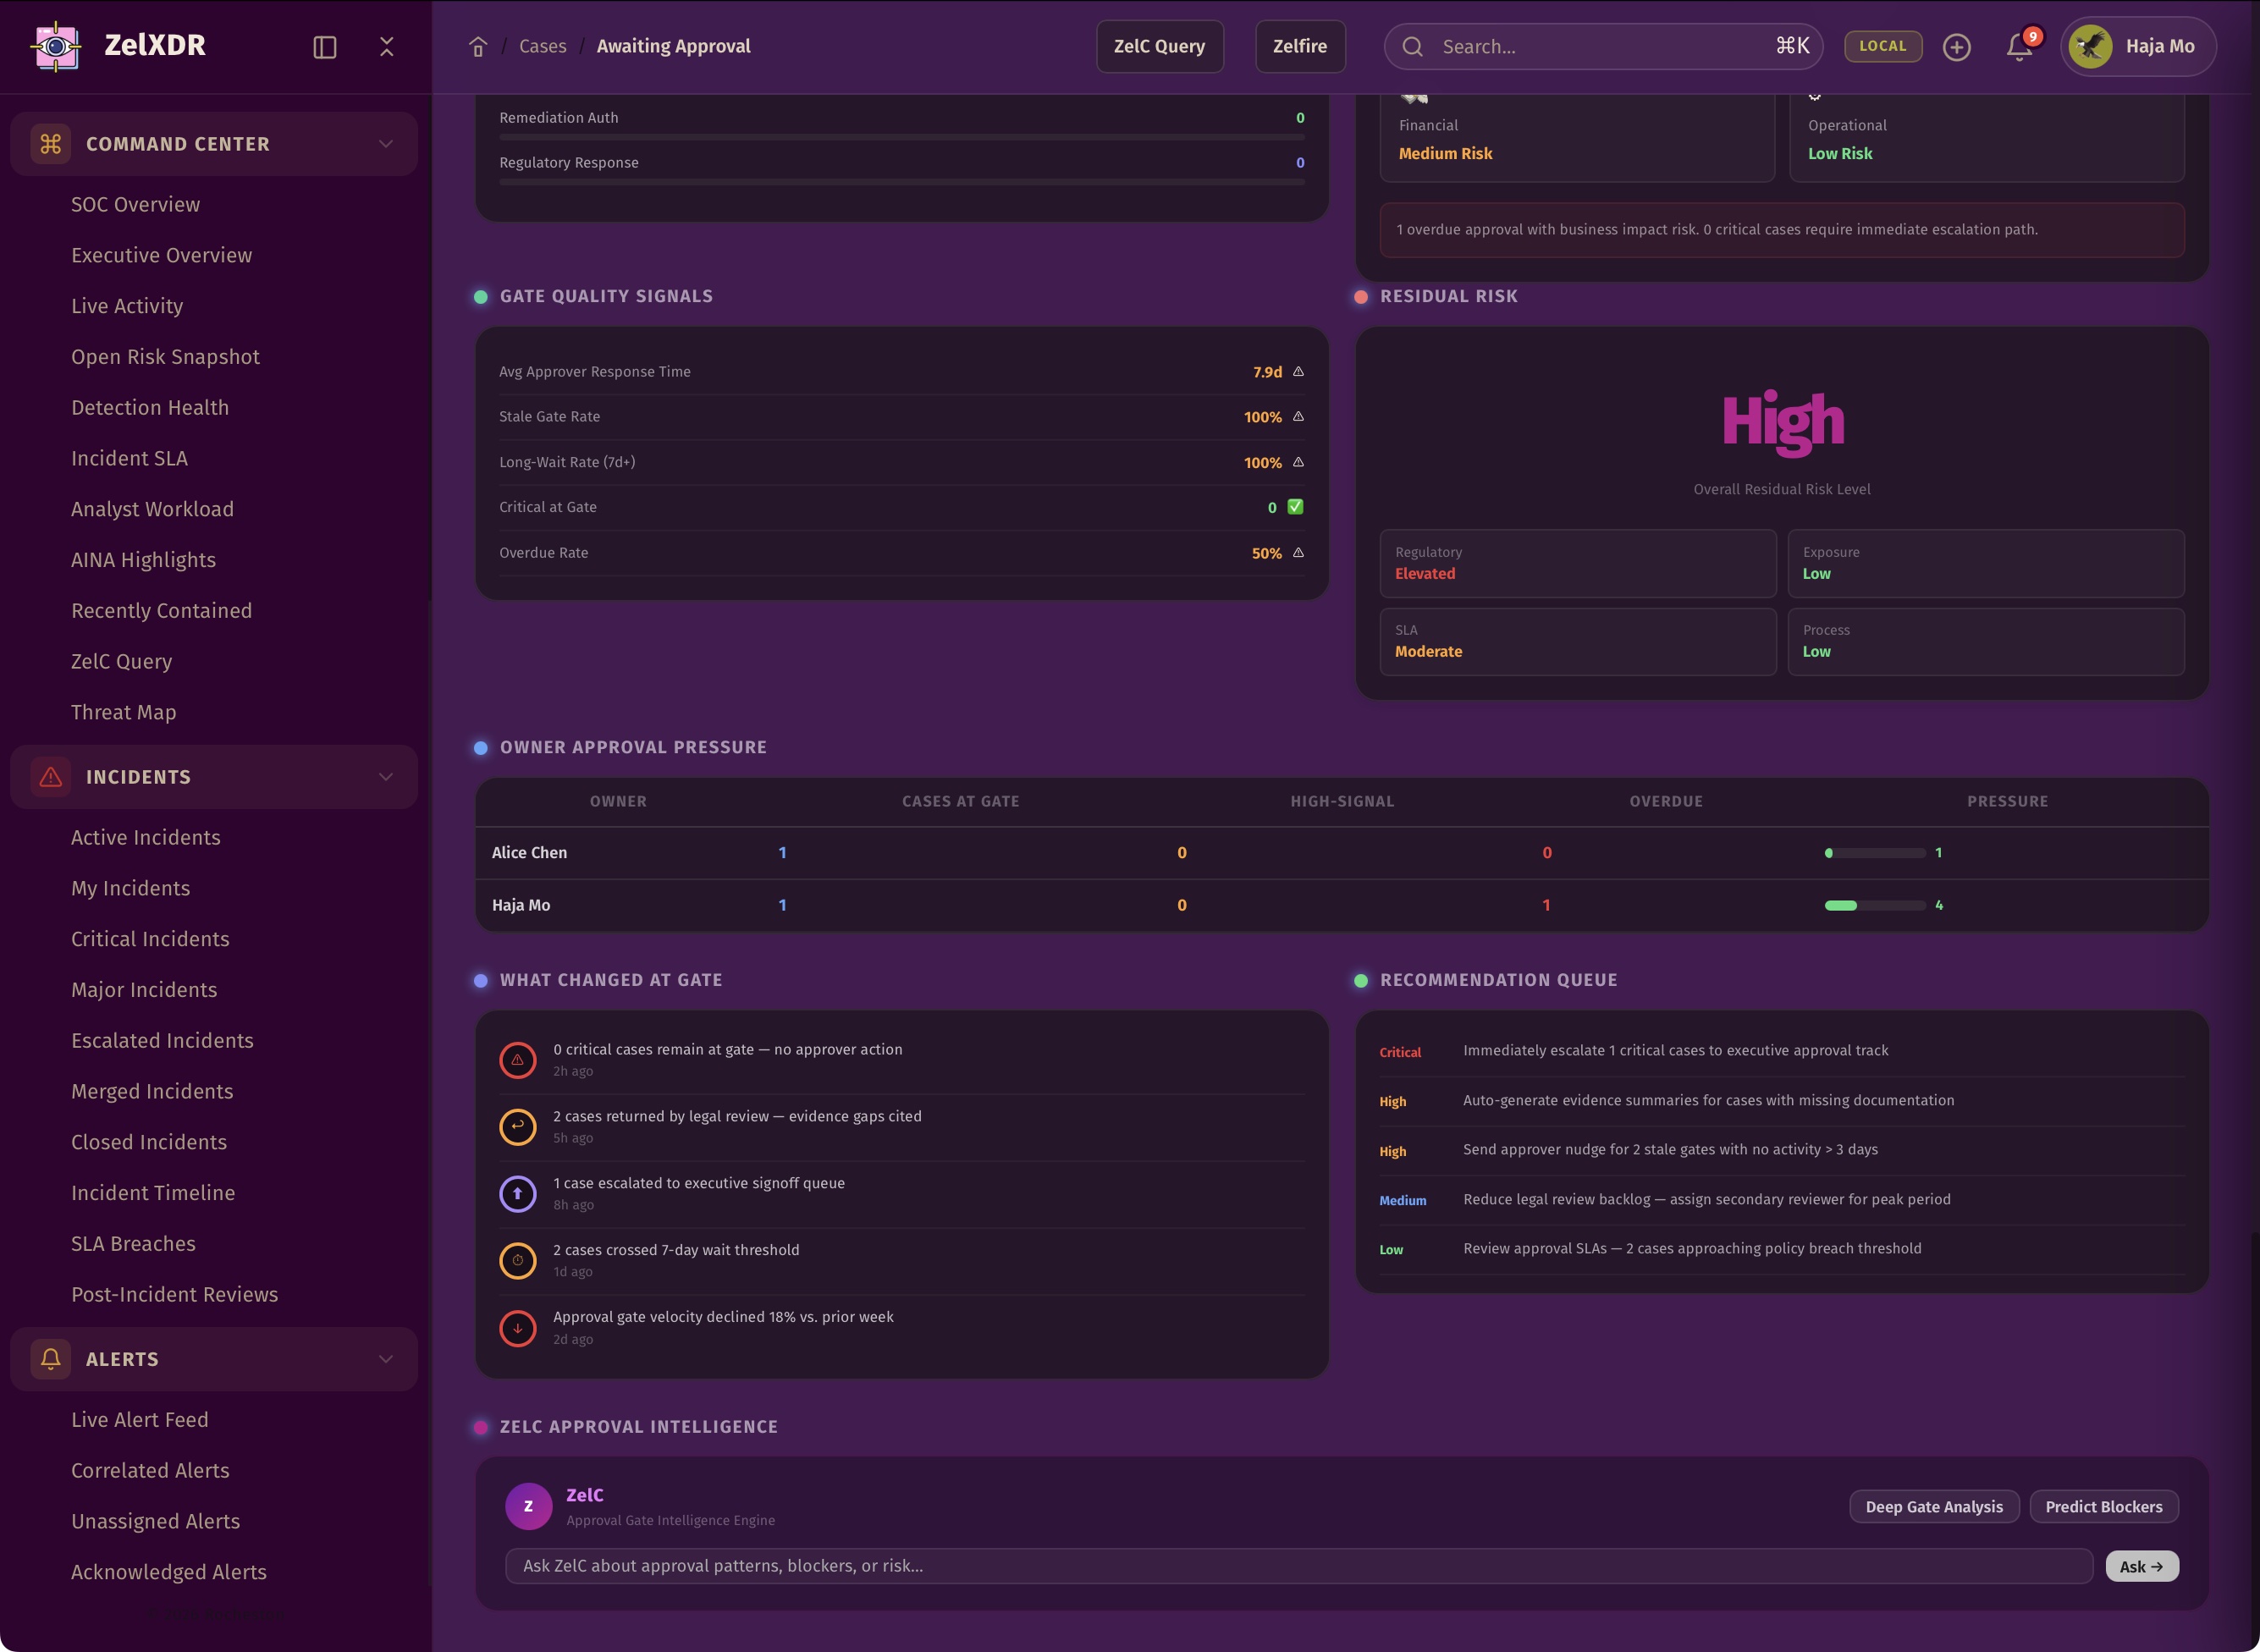
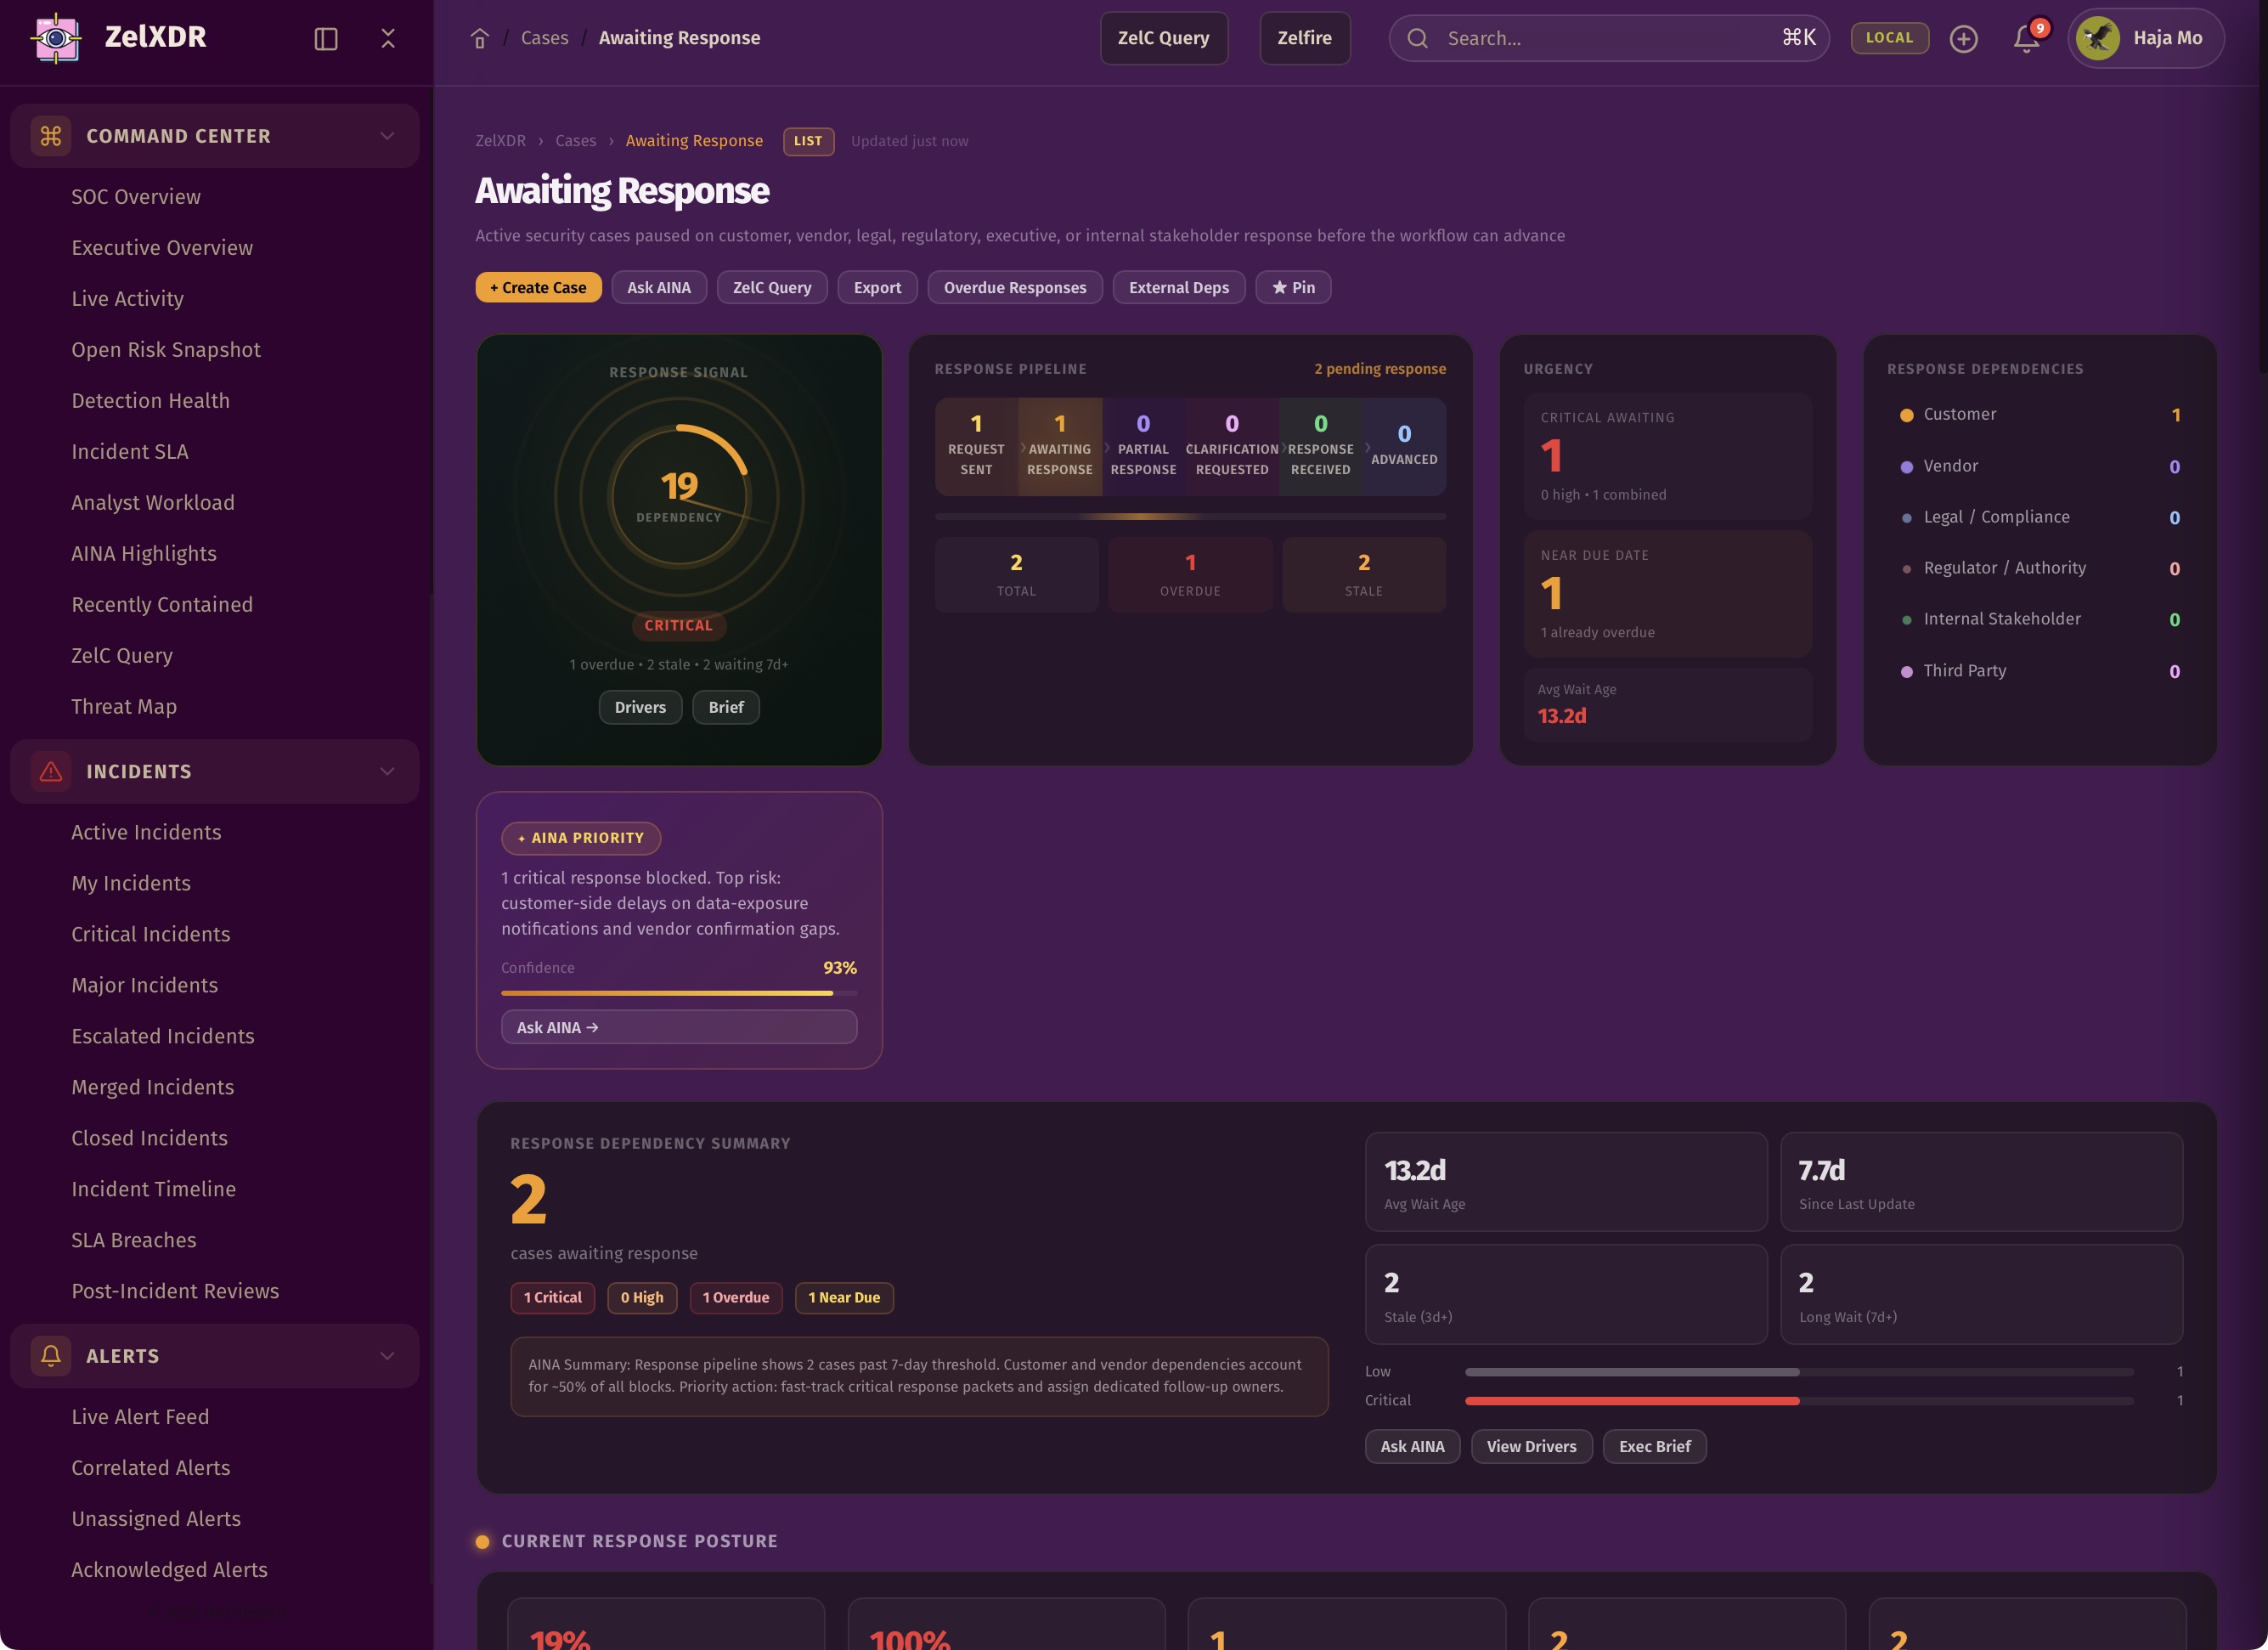
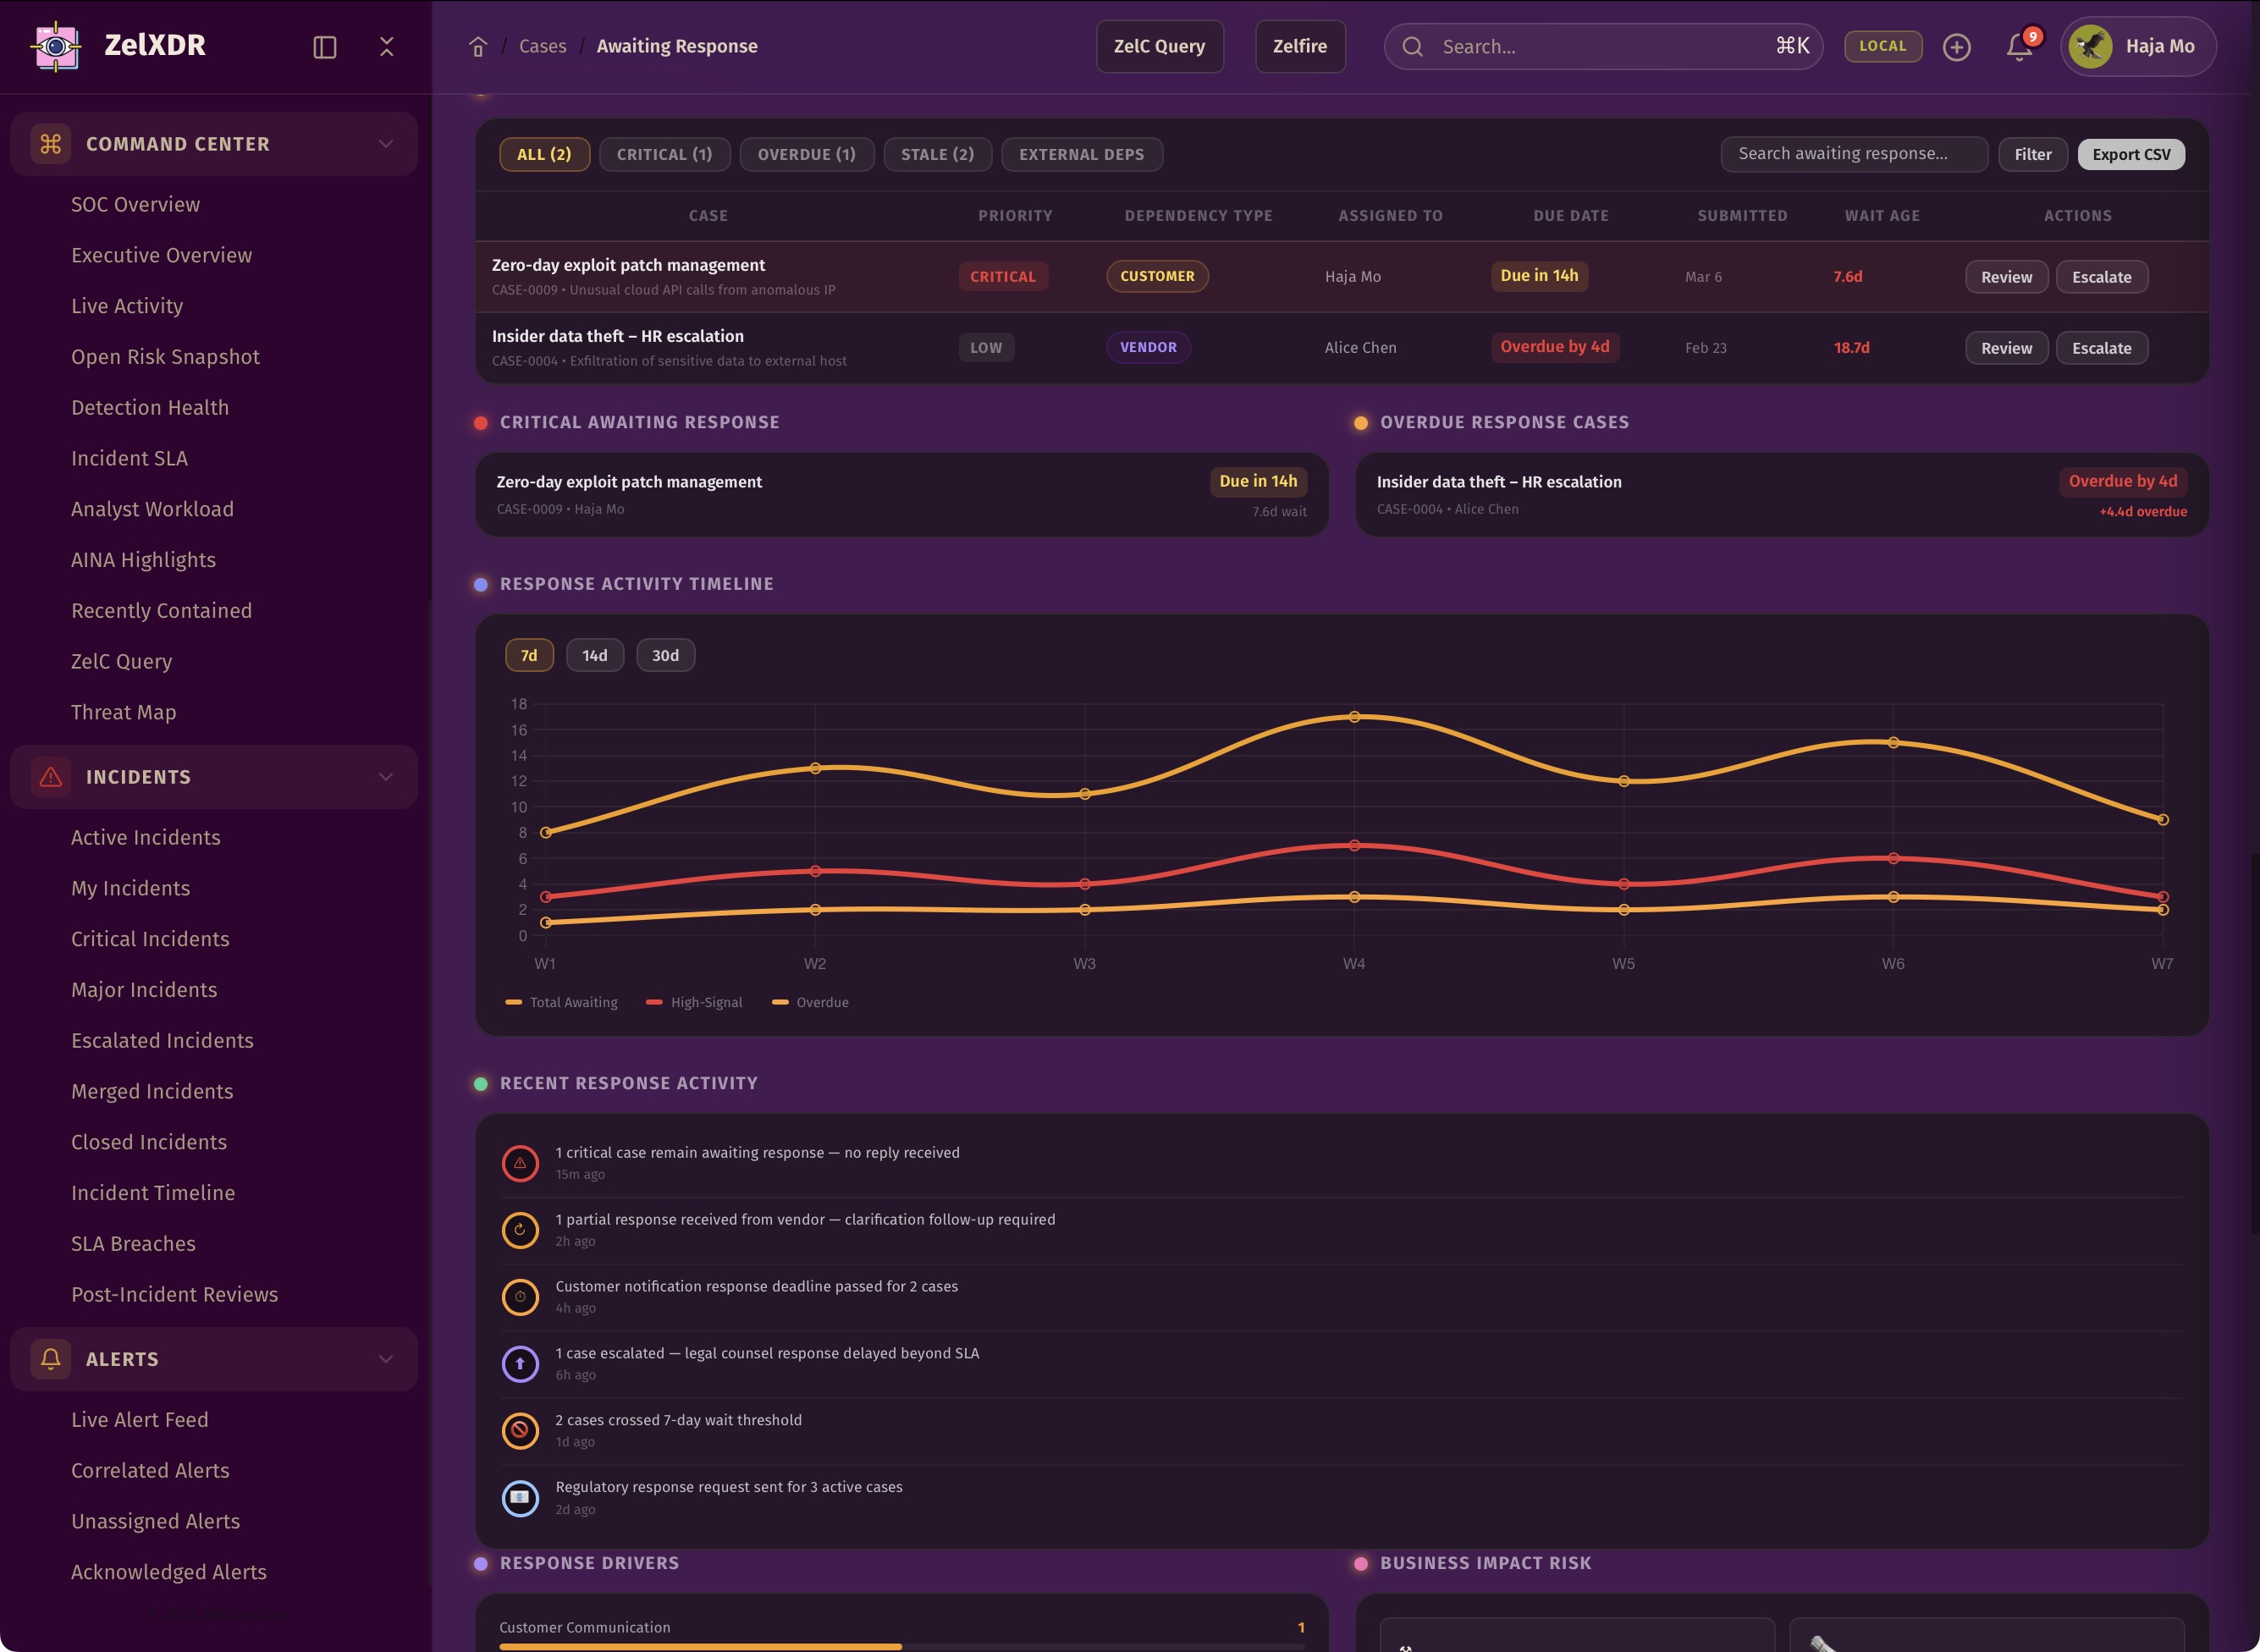
THE DETAILS THAT MATTER
Answers about the product, its capabilities, and how it fits into your security workflow.
ZelXDR is an AI-powered extended detection and response platform in the Zelfire ecosystem. It unifies alerts, incidents, investigations, threat hunting, telemetry, endpoint visibility, vulnerability intelligence, reporting, response workflows, and AI-driven reasoning into one operational environment. ZelXDR is designed to help security teams move from raw signal to context, from context to decision, and from decision to action.
ZelXDR helps organizations detect threats, investigate suspicious activity, triage alerts, analyze incidents, manage endpoints, study telemetry, perform threat hunts, review vulnerabilities, build detections, and generate reports. It is designed to bring multiple security workflows into one platform so teams do not have to jump between disconnected tools. The platform is built to reduce noise, accelerate understanding, and improve response quality.
ZelXDR is designed as an operational command platform, not just an alert viewer. It combines AI reasoning through AINA, detection engineering, threat hunting, entity pivots, baseline analysis, anomaly investigation, endpoint control, reporting, integrations, and administrative governance in one place. The goal is not only to collect security signals, but to help users understand them, explain them, and act on them.
ZelXDR was created by Haja Mo as part of the broader Zelfire cybersecurity ecosystem. It reflects a unified design philosophy where security operations, AI reasoning, automation, hunting, reporting, and governance are treated as parts of the same platform instead of separate product silos.
Zelfire is the broader cybersecurity product family and ecosystem that includes ZelXDR and related security products. It is positioned as a connected ecosystem of security technologies covering detection, response, threat intelligence, endpoint control, posture, reporting, analytics, AI, and operational workflows. ZelXDR is one of the core operational products inside that ecosystem.
ZelXDR is part of the Zelfire family of products. Zelfire is the wider ecosystem, while ZelXDR is the platform focused on extended detection, investigation, response, and security operations. The relationship is similar to a flagship platform inside a larger security portfolio.
Haja Mo is the creator behind ZelXDR, Zelfire, AINA, and ZelC. In this product narrative, Haja Mo is the builder and architect of the platform ecosystem, including the AI reasoning layer, the operational workflows, the reporting system, and the security language experience tied to ZelC.
AINA is the AI intelligence layer inside the Zelfire ecosystem and a major intelligence layer inside ZelXDR. AINA assists with alert triage, incident summaries, root cause reasoning, blast radius estimation, MITRE mapping, executive summaries, analyst note generation, hunt guidance, and next-step recommendations. AINA is meant to reduce analyst overload while improving clarity and decision quality.
ZelC is the cybersecurity-native language associated with the Zelfire ecosystem and used in ZelXDR experiences such as ZelC Query. It is positioned as a specialized language for querying, operational workflows, investigative commands, platform interaction, and security reasoning. ZelC is meant to feel native to cyber operations rather than like a generic programming language.
ZelXDR is closely tied to the RCCE ecosystem in the way it is positioned and described. The platform is presented as part of a broader advanced cybersecurity engineering environment connected to RCCE use cases, workflows, and exclusive product access.
Yes. The platform positioning states that Zelfire is exclusively licensed to RCCE engineers. That means the Zelfire product family, including ZelXDR-related experiences, is presented as an ecosystem reserved for RCCE engineers rather than general public distribution.
RCCE is presented as an advanced cybersecurity war school environment connected to the Zelfire ecosystem. In this positioning, RCCE engineers gain access to Zelfire products and operational tooling, making ZelXDR part of a broader cybersecurity training, engineering, and execution environment.
No. ZelXDR is not just a dashboard or alert console. It is an operational platform that combines detection, AI triage, hunting, telemetry exploration, endpoint control, reporting, investigation workflows, governance, and integrations into one unified security surface.
ZelXDR is designed for analysts, threat hunters, incident responders, detection engineers, SOC leads, platform administrators, security managers, and executive stakeholders. Different parts of the platform serve different users, but the whole system is designed to keep everyone working from the same security truth.
ZelXDR unifies alerts, incidents, investigations, cases, detections, threat hunts, telemetry, endpoints, identities, cloud activity, network activity, email security, threat intelligence, AI reasoning, reporting, integrations, and governance controls. The purpose is to reduce fragmentation and create a continuous workflow from signal to action.
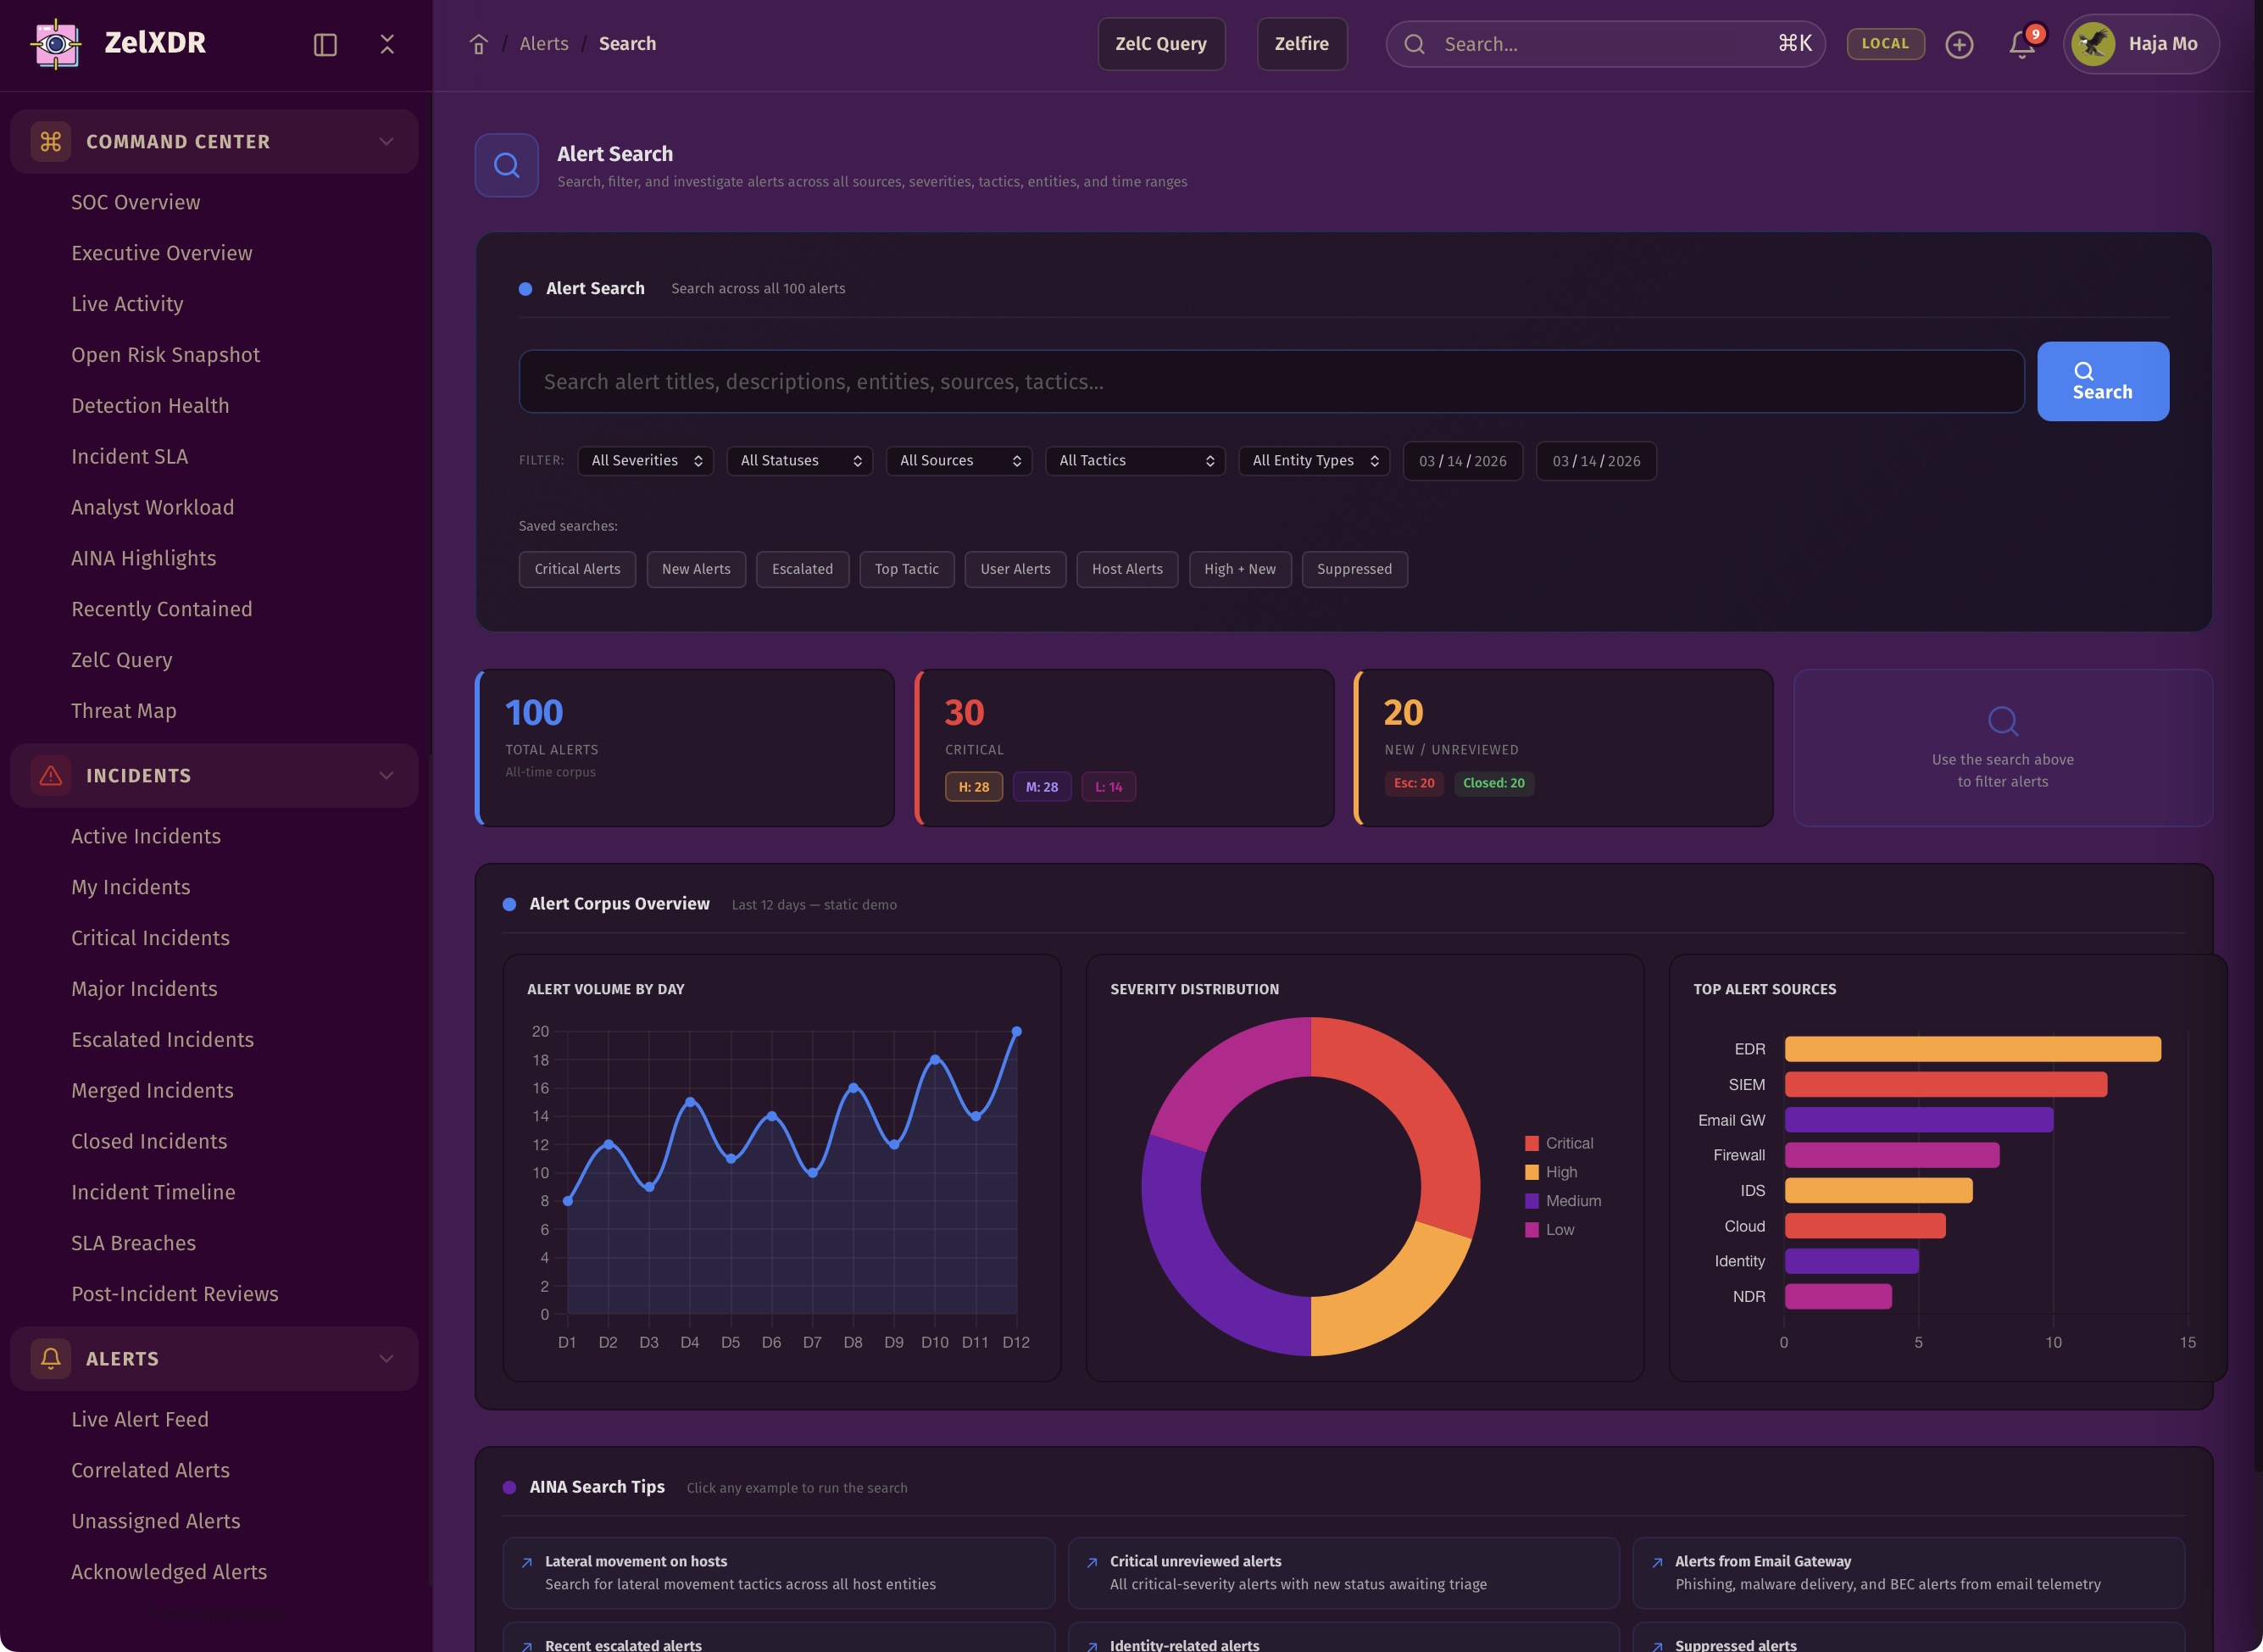
Yes. Alert triage is a core ZelXDR function. The platform is designed to let users review alerts, cluster related alerts, find duplicates, identify likely false positives, connect alerts to entities and incidents, and use AINA to explain what matters and what should happen next.
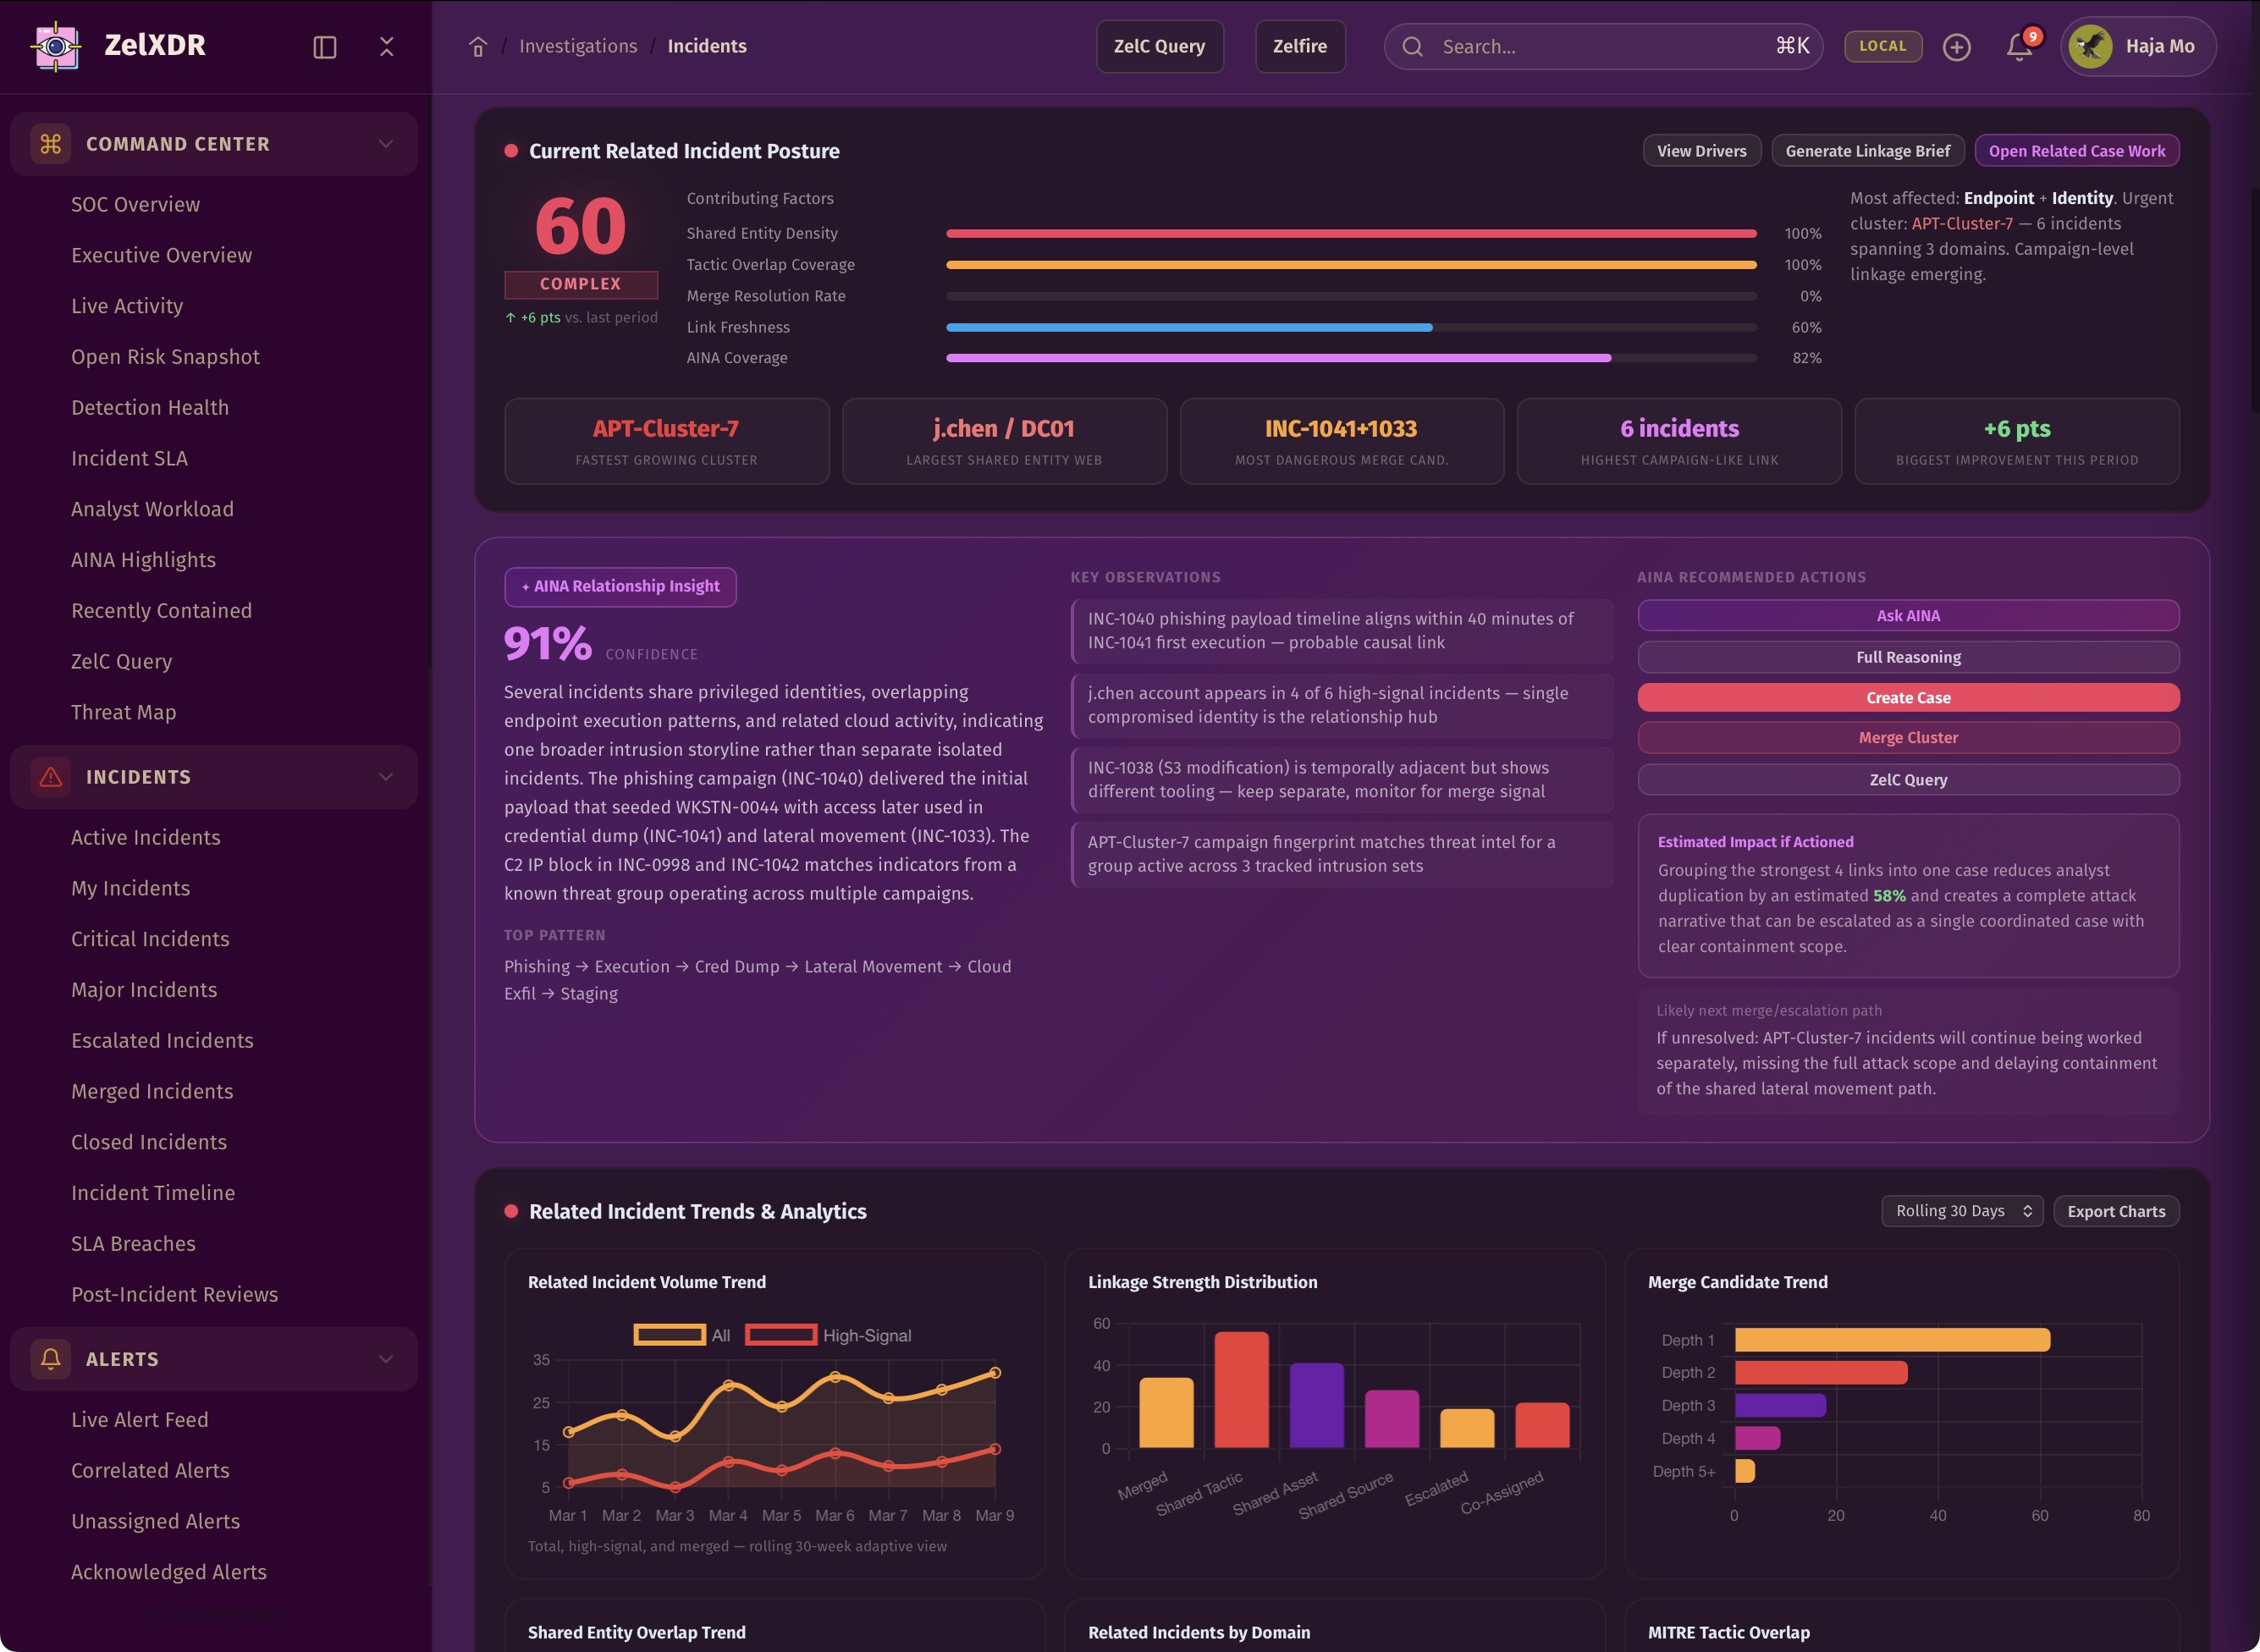
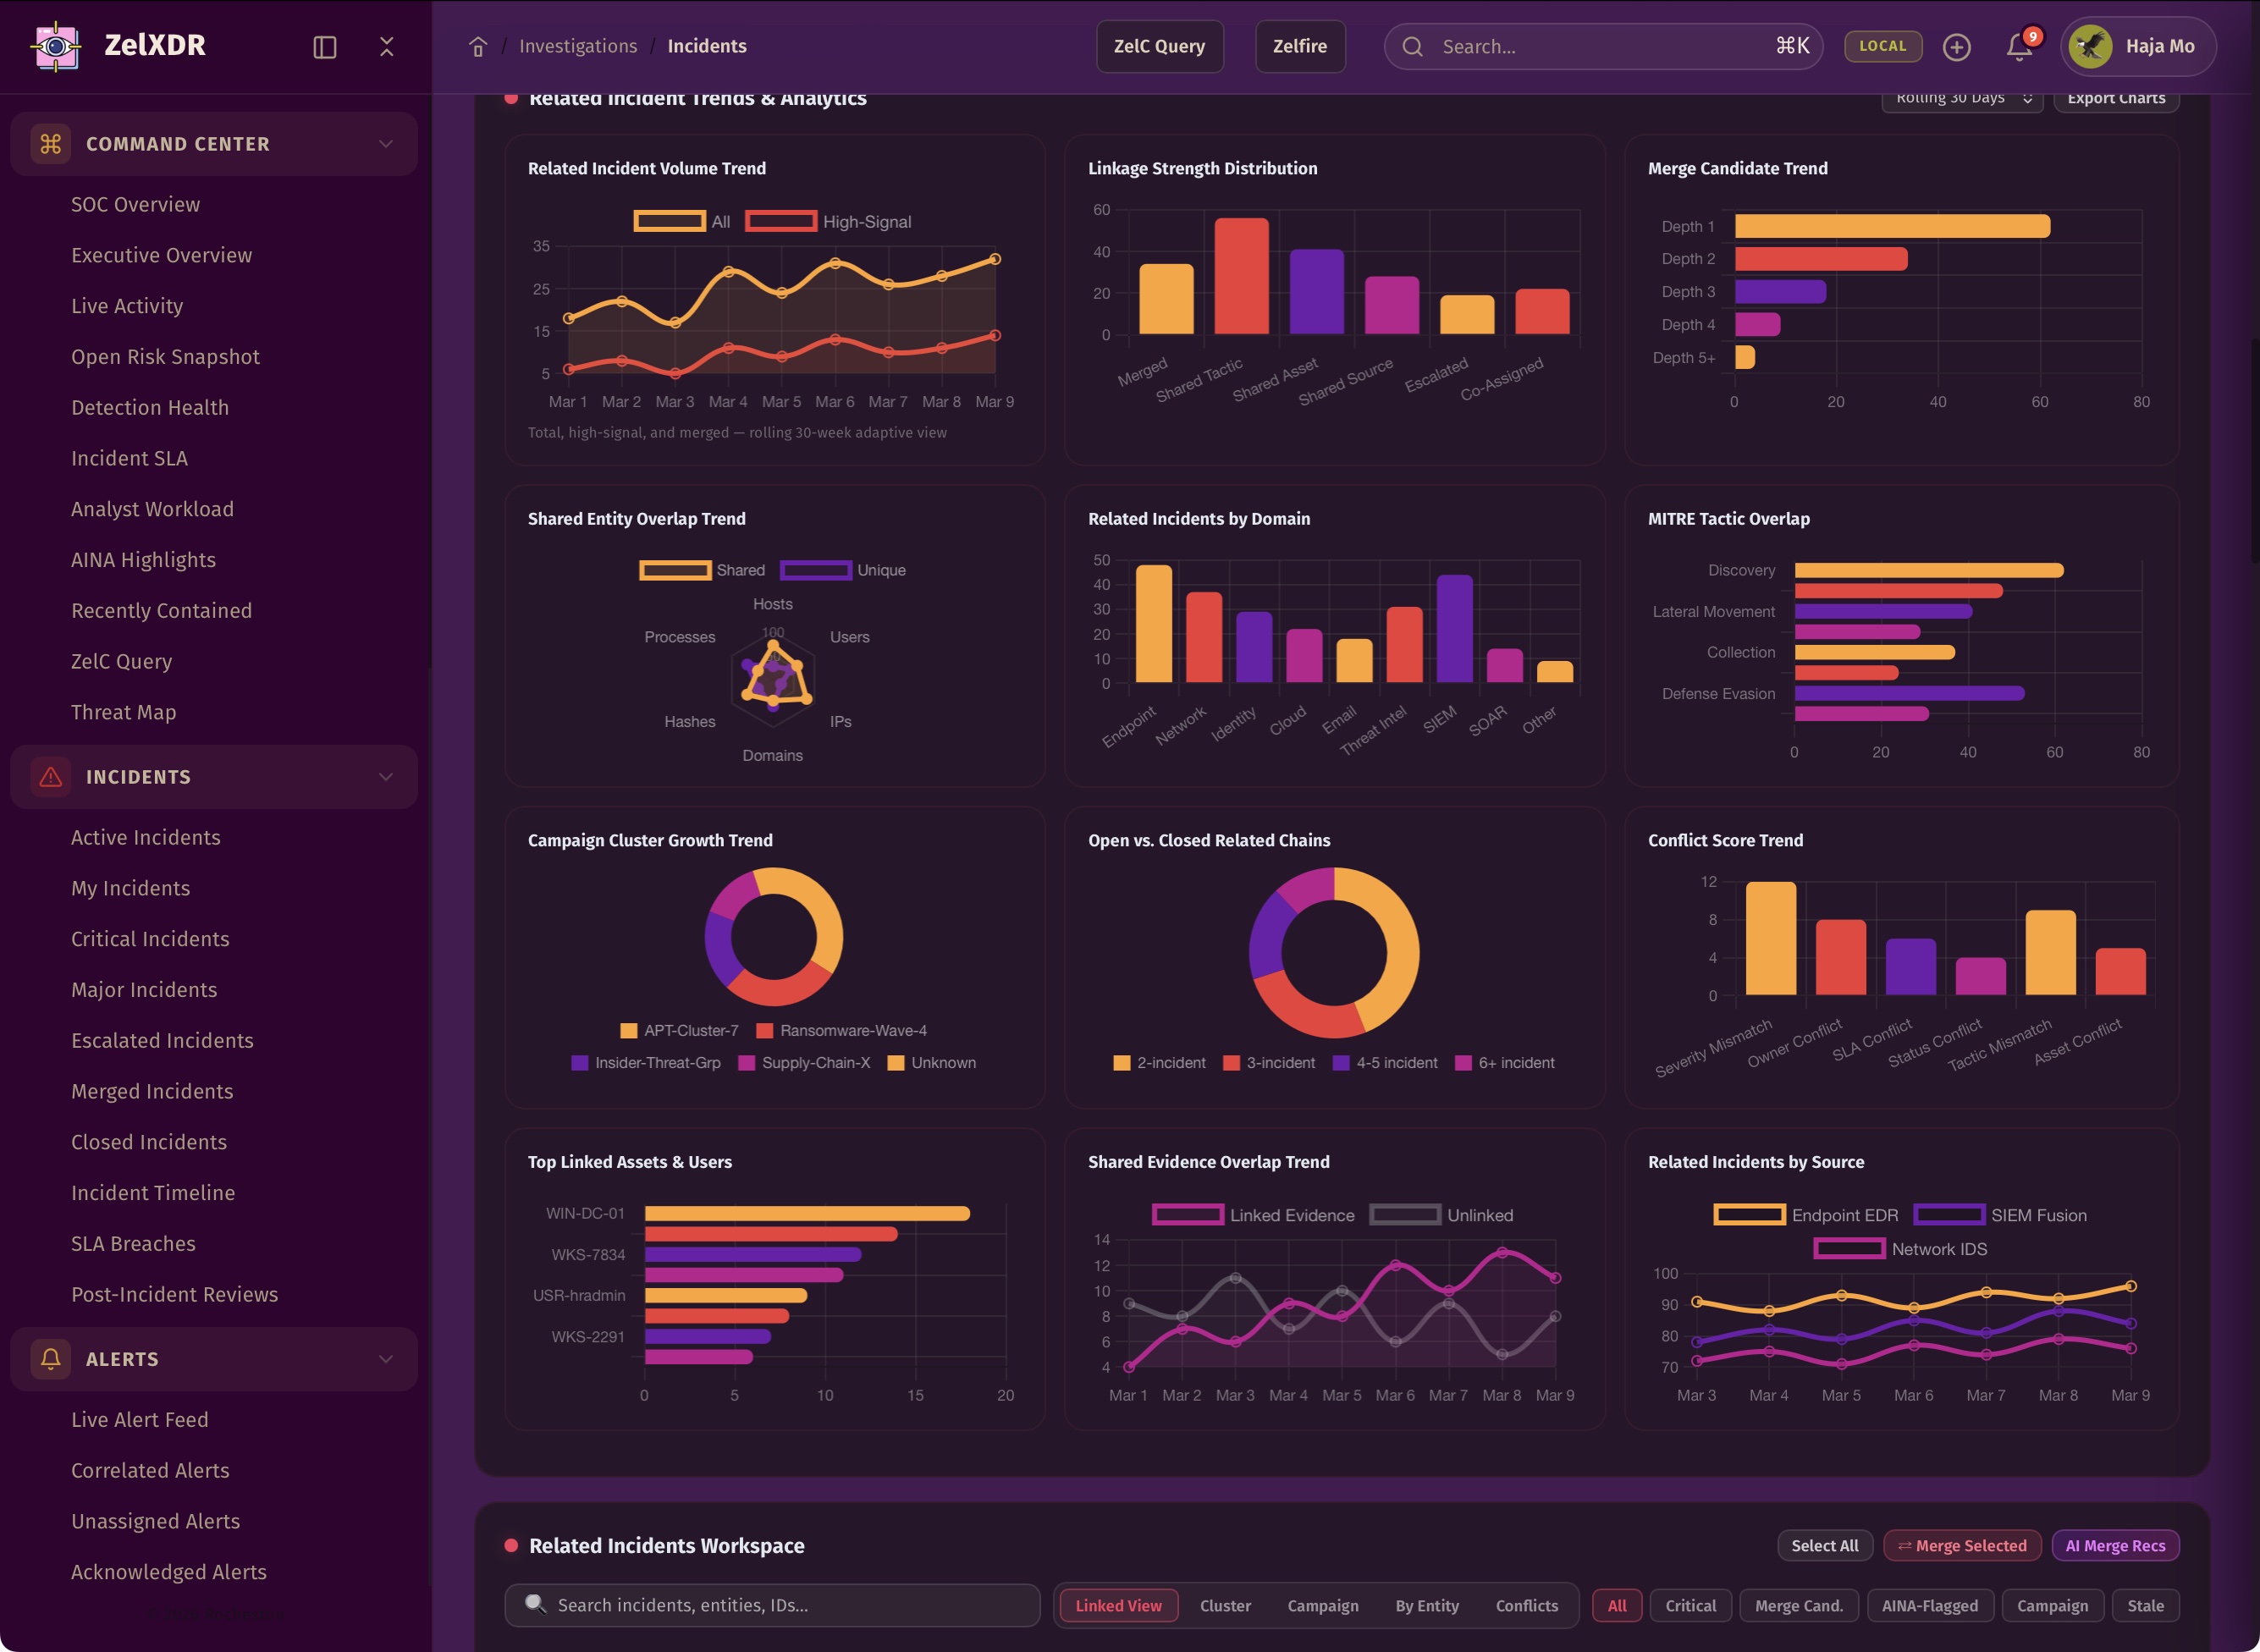
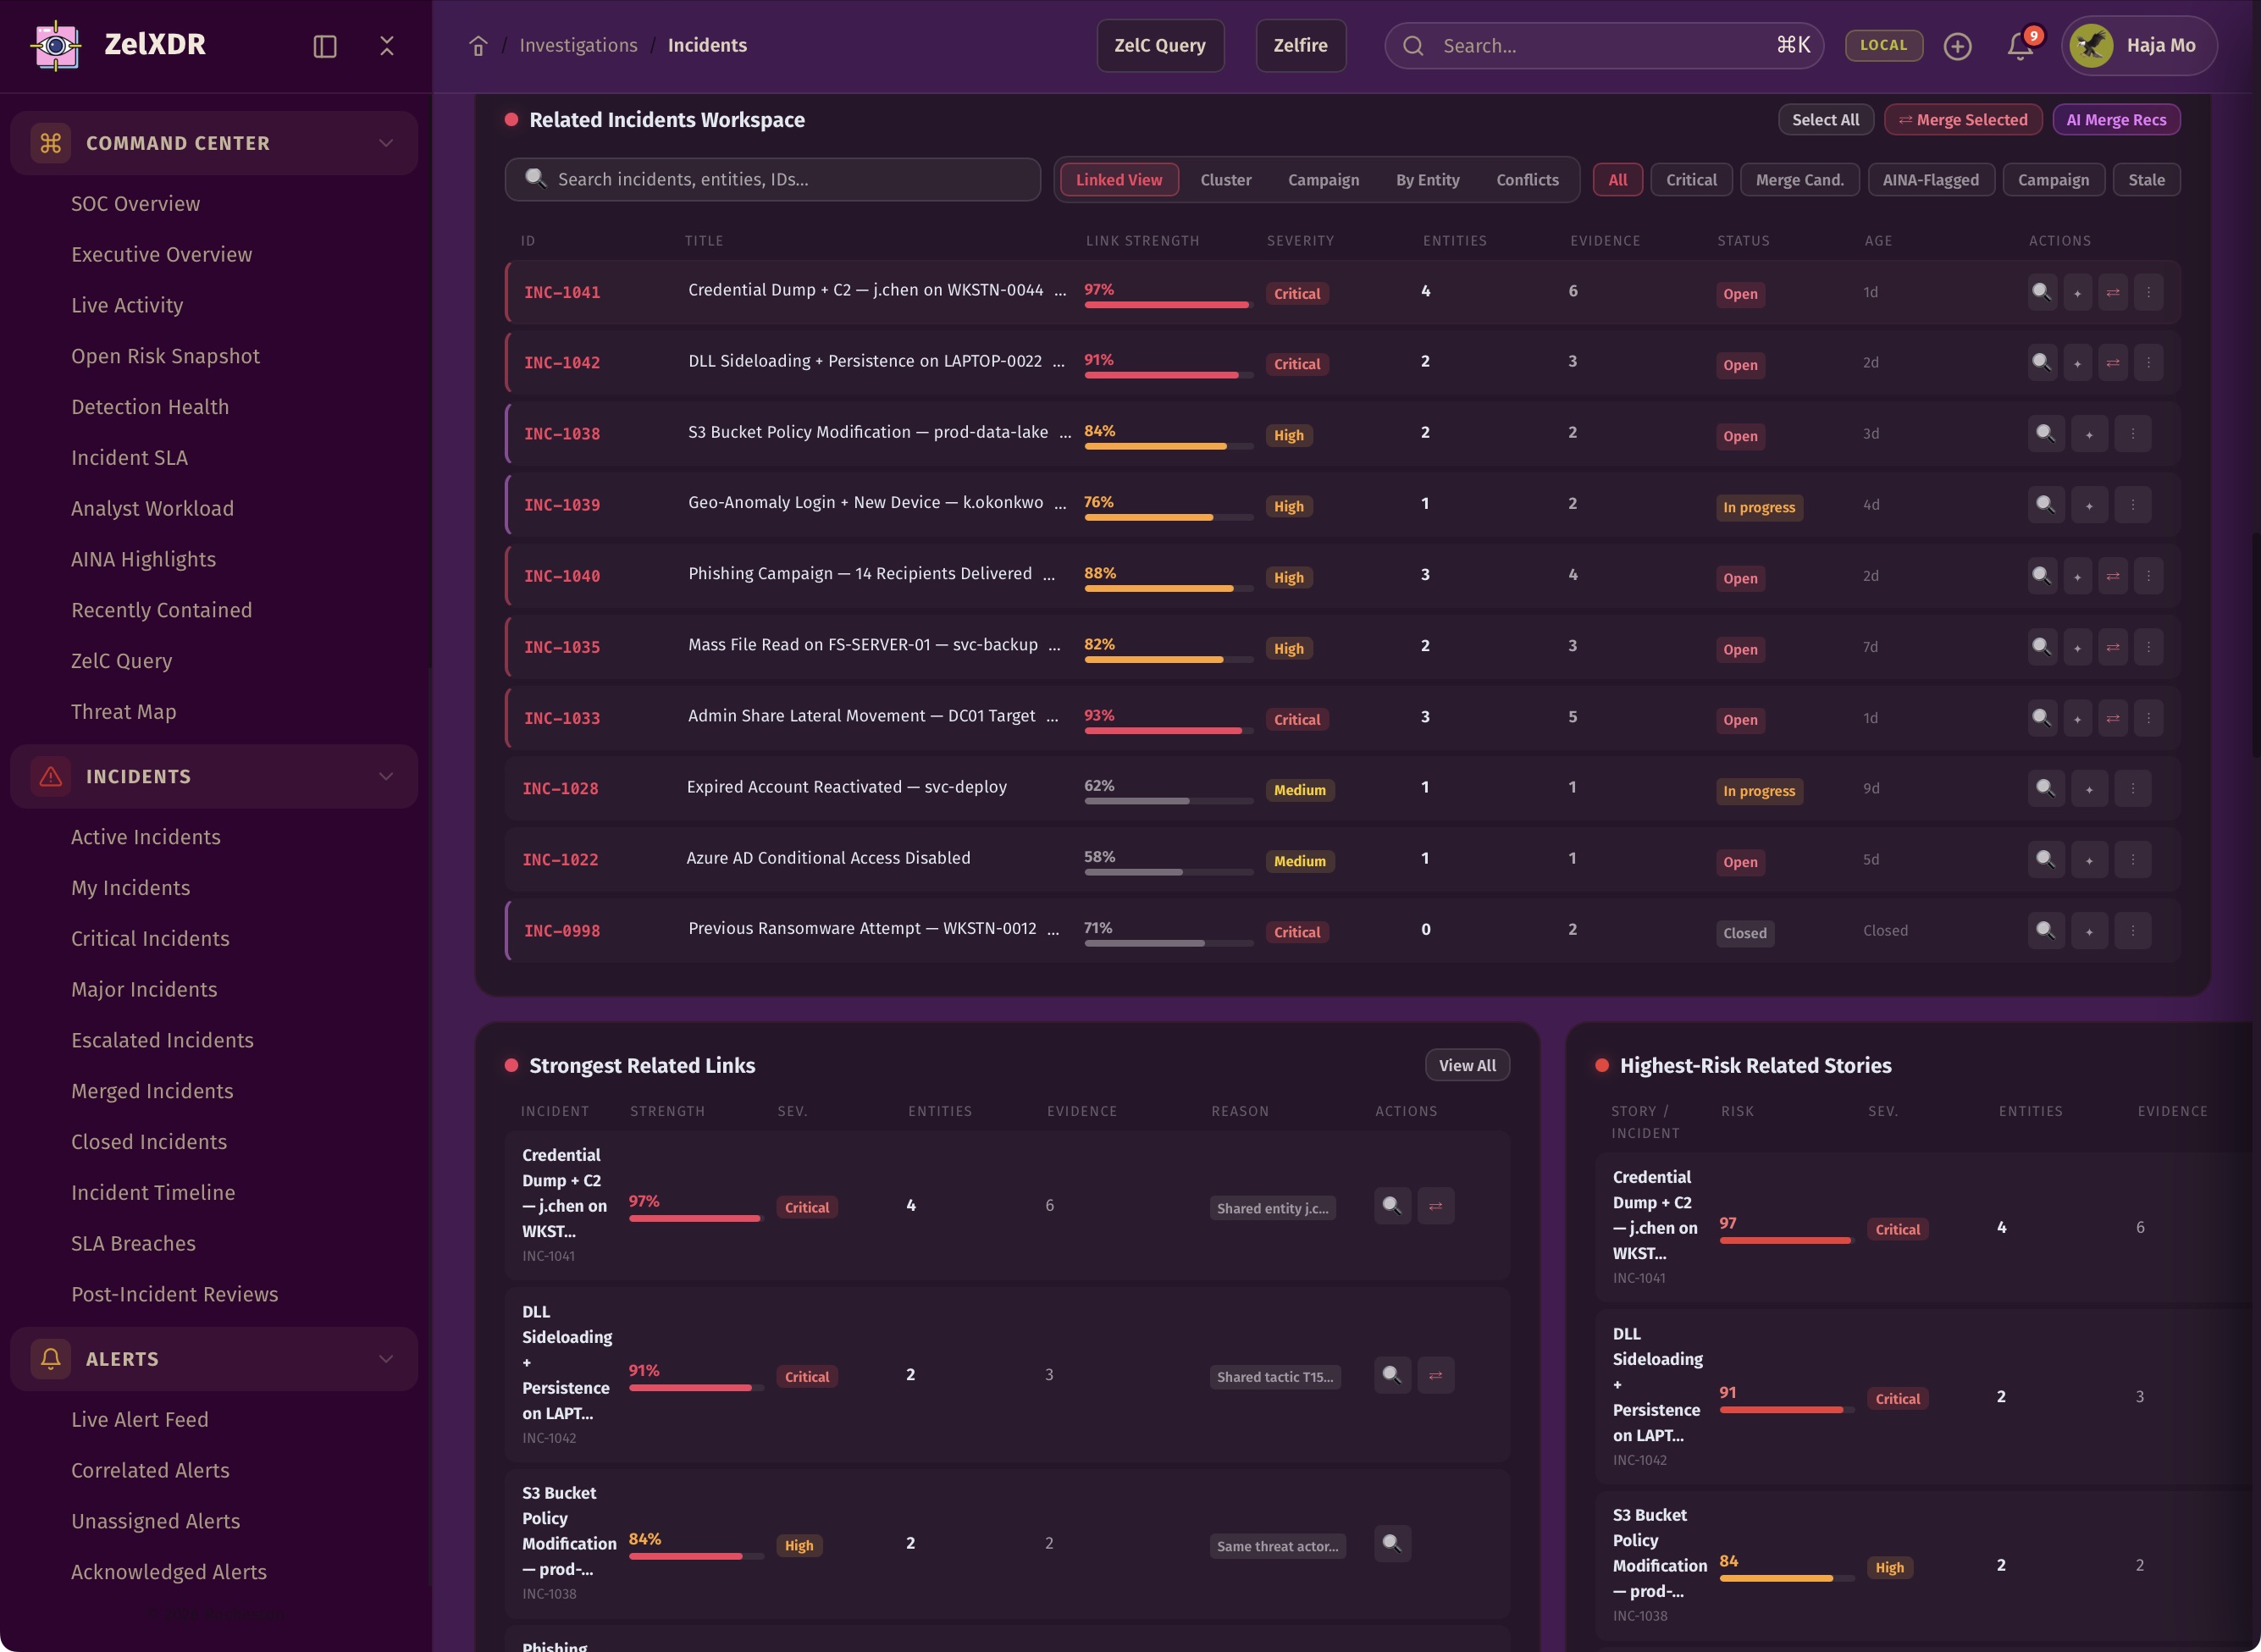
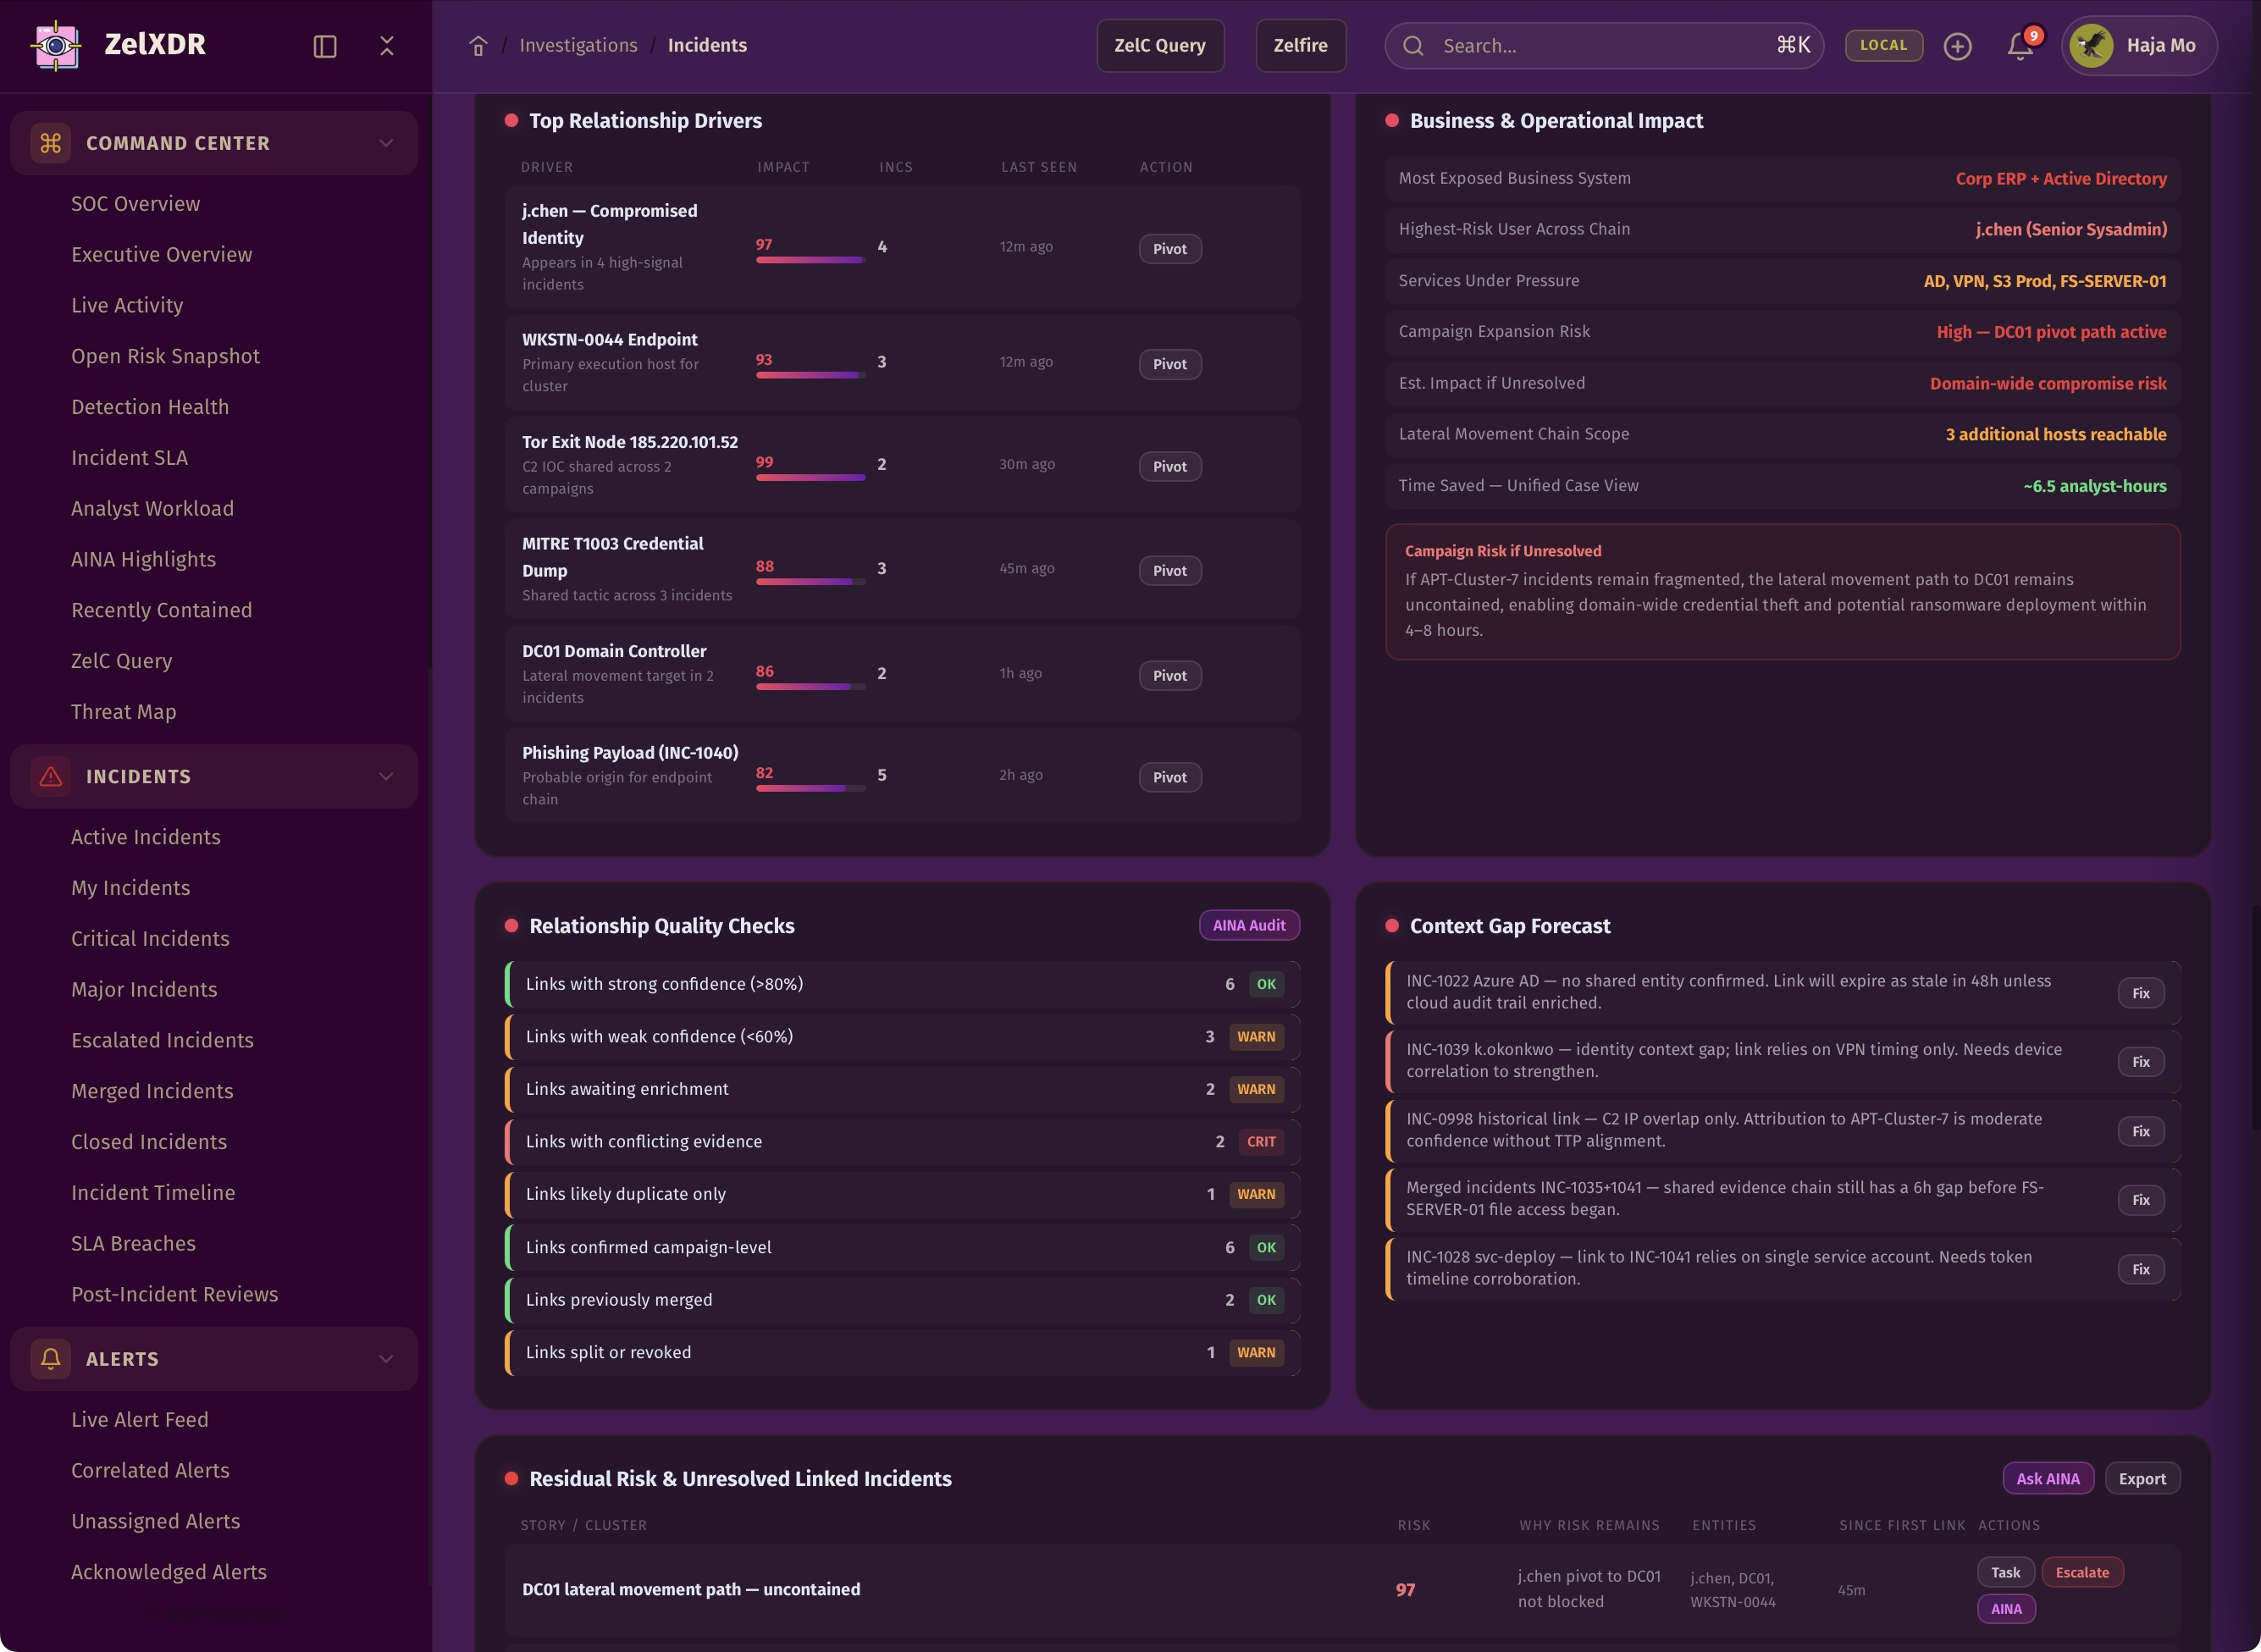
Yes. Incident analysis is one of the core experiences in ZelXDR. The platform is designed to help summarize incidents, explain why they matter, estimate impact, show linked evidence, reveal blast radius, recommend containment actions, and generate both analyst-facing and executive-facing summaries.
Yes. Through AINA and linked incident intelligence workflows, ZelXDR is designed to explain why an incident matters, how it connects to business impact, what evidence supports it, which assets and users are involved, and what the recommended next steps are.
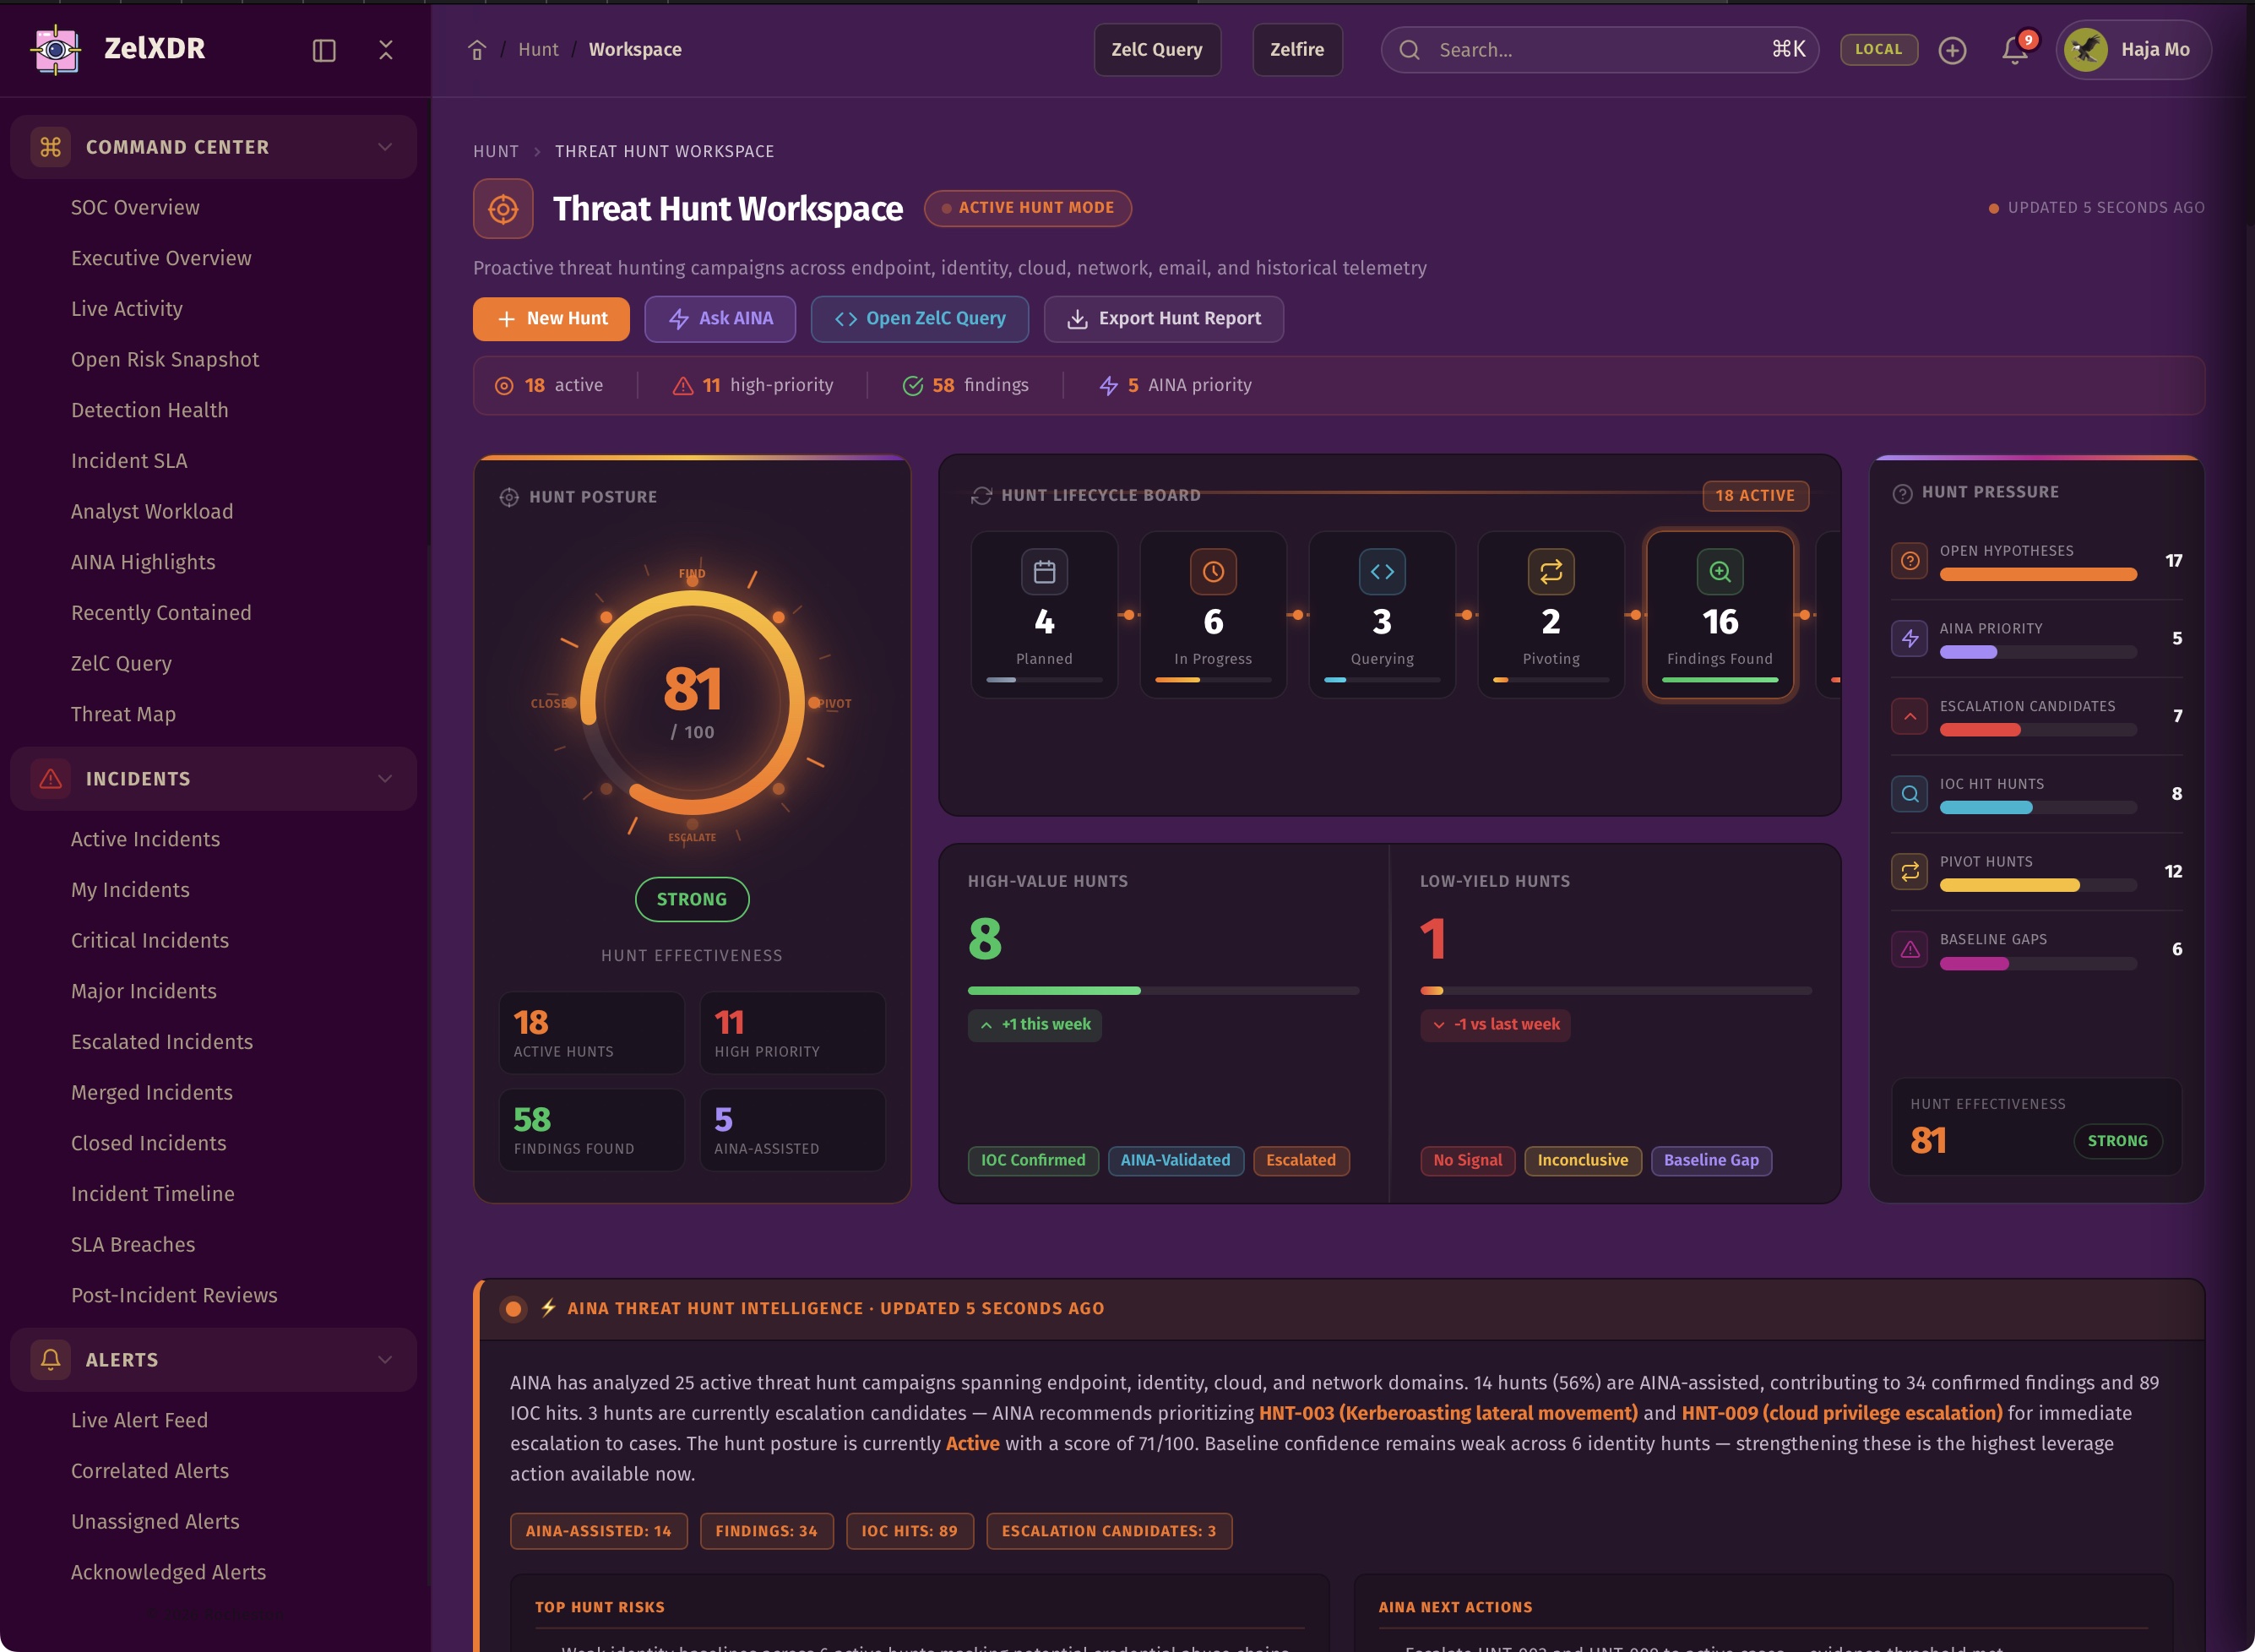
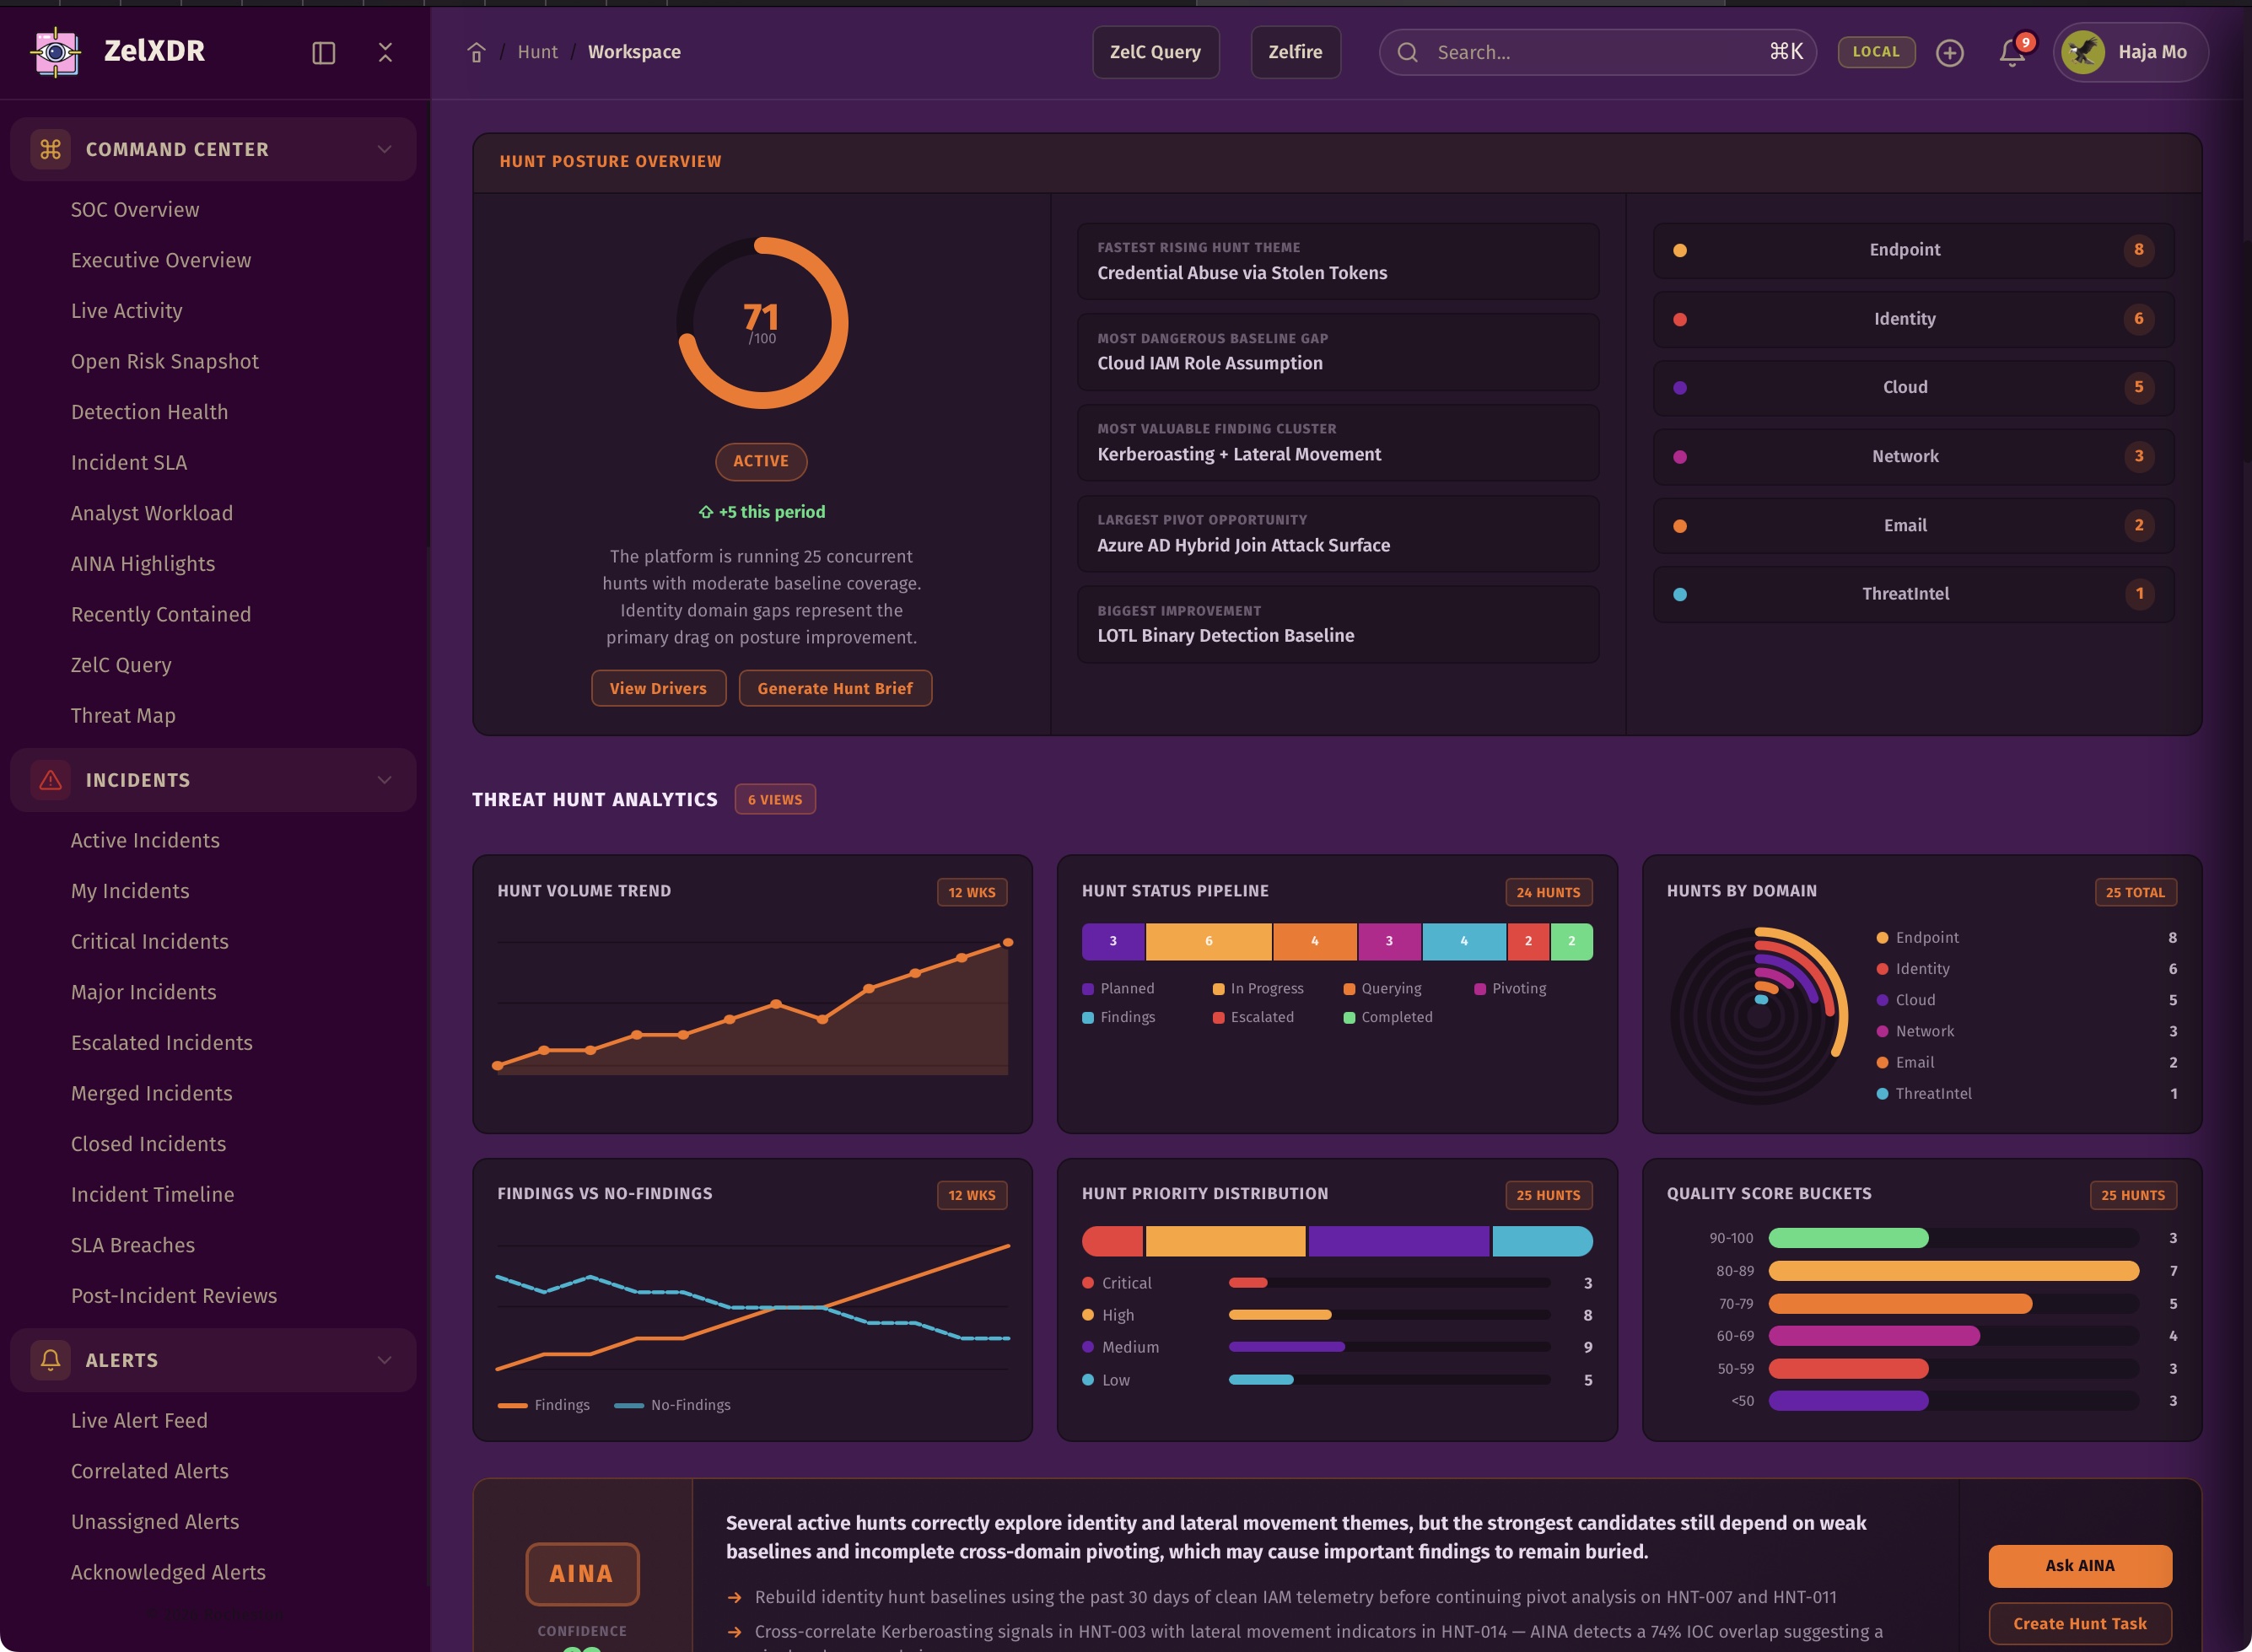
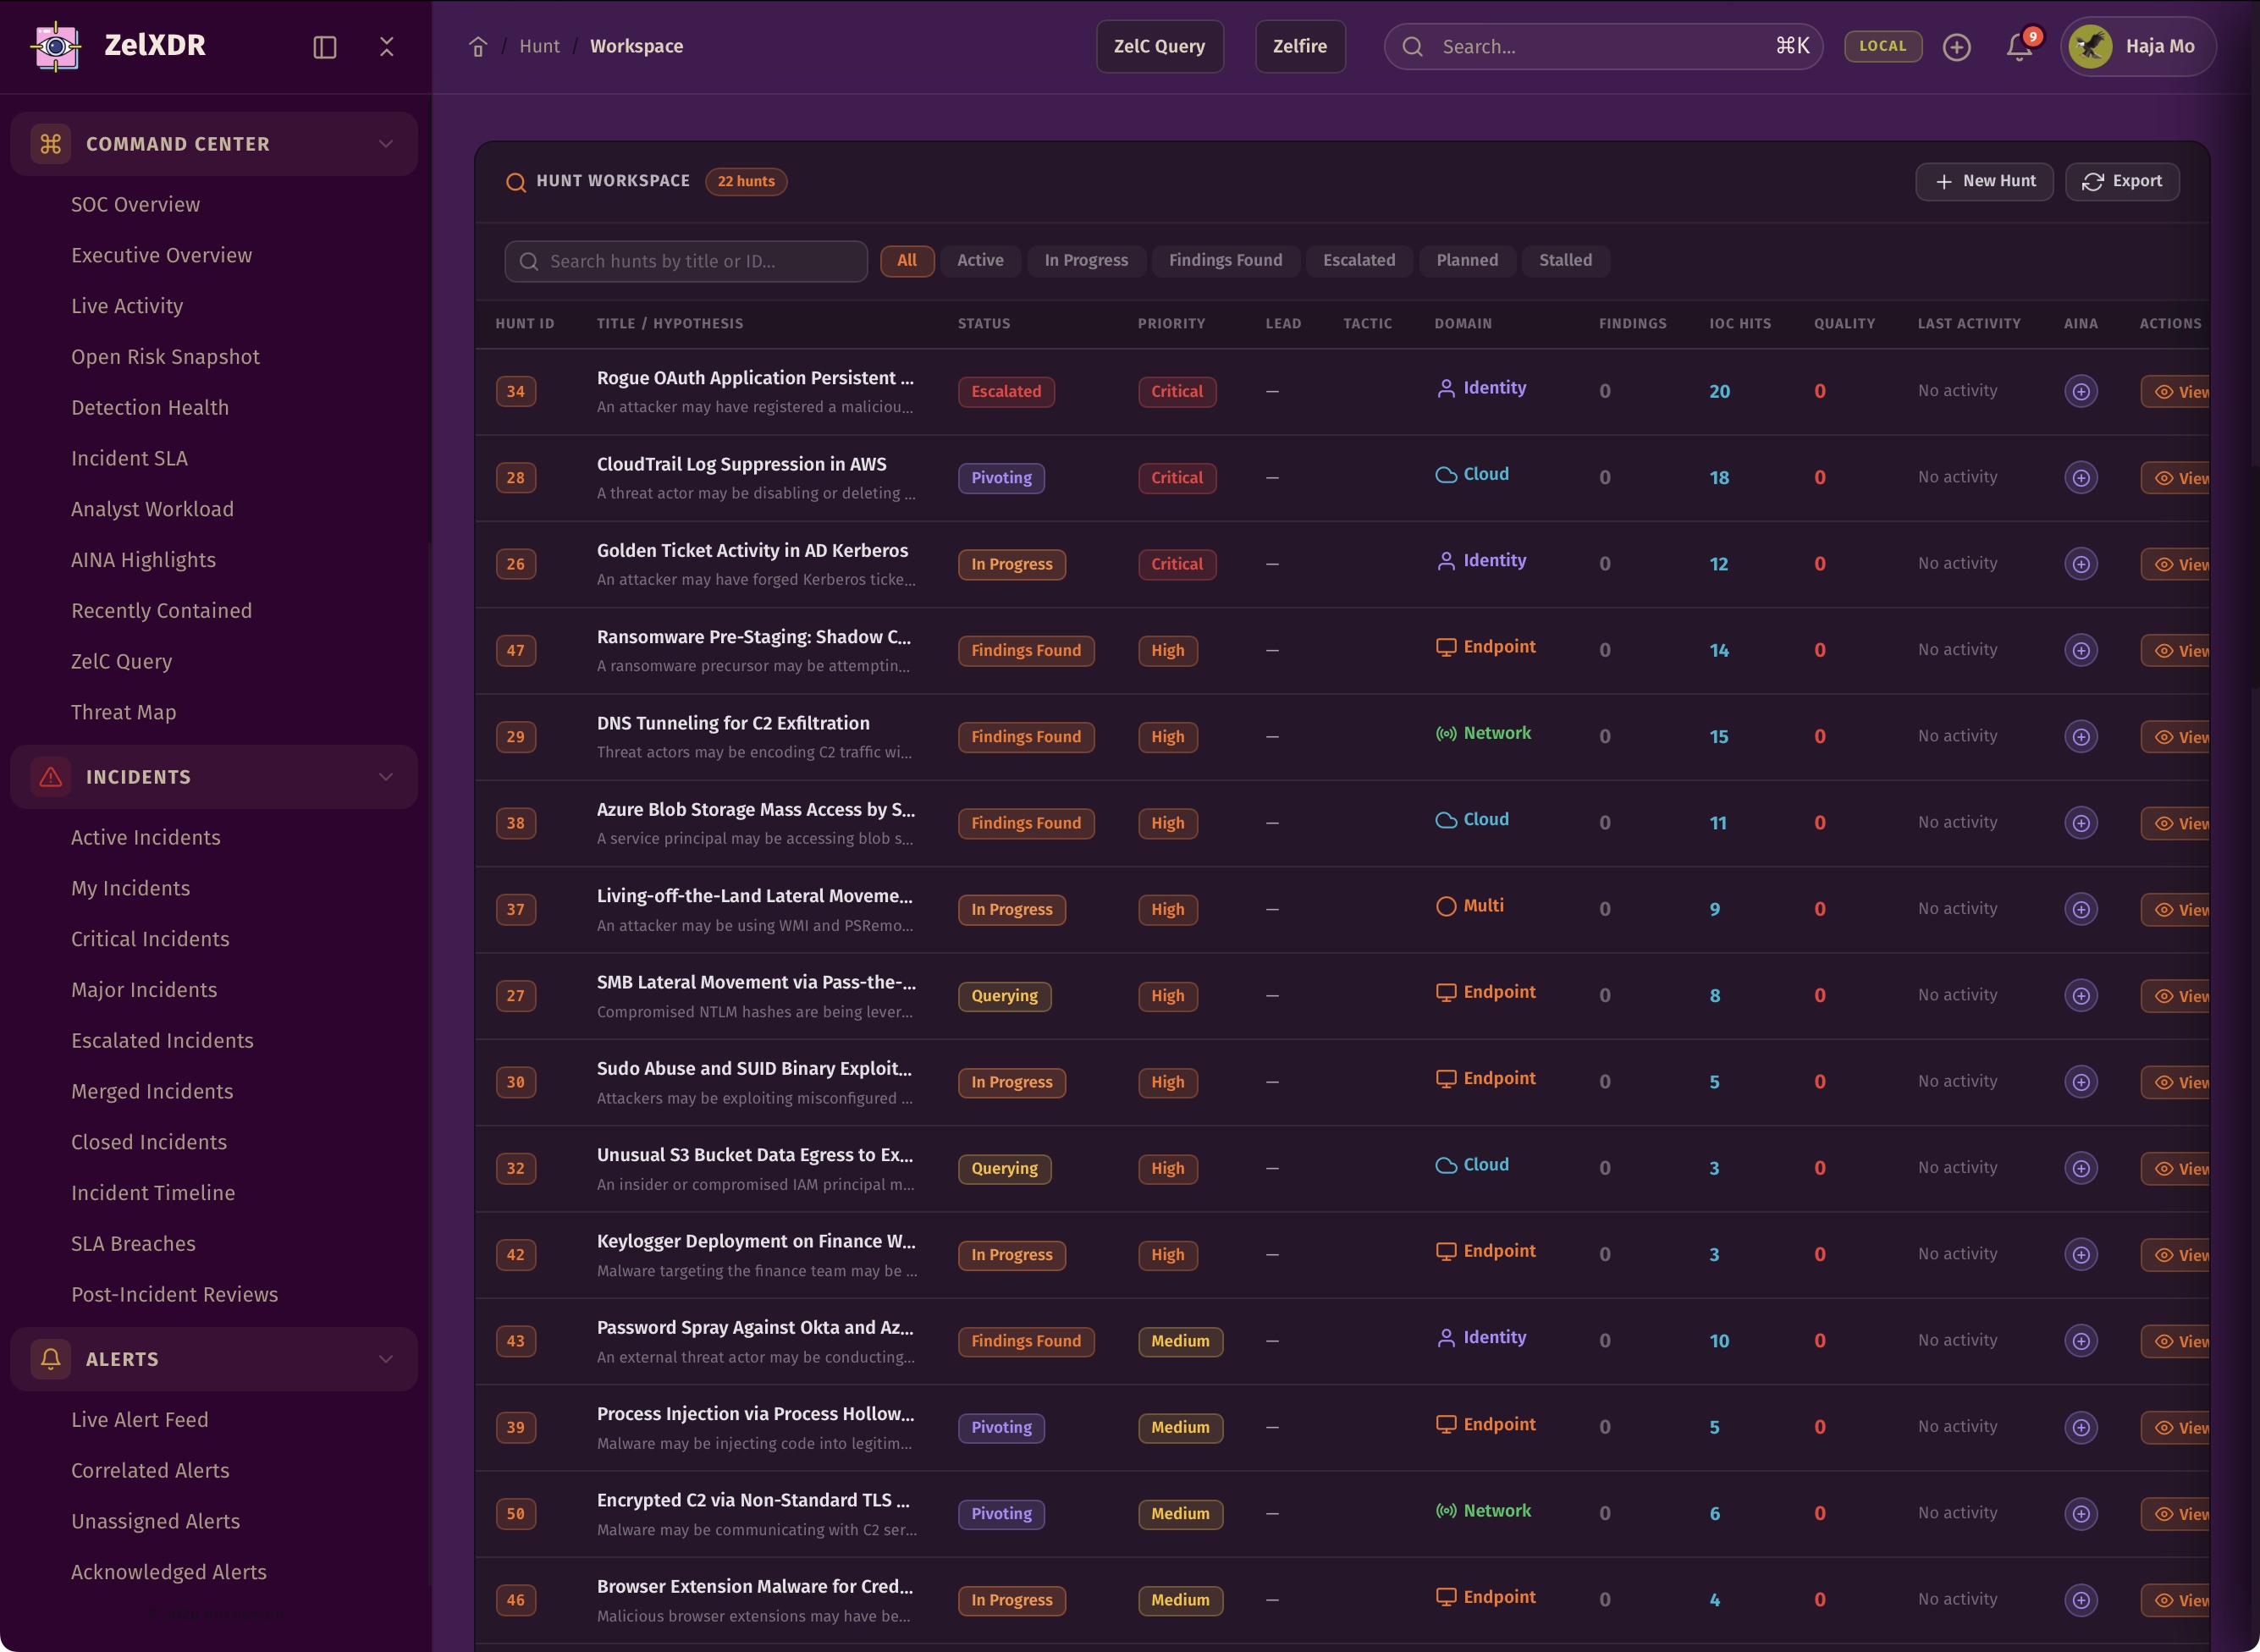
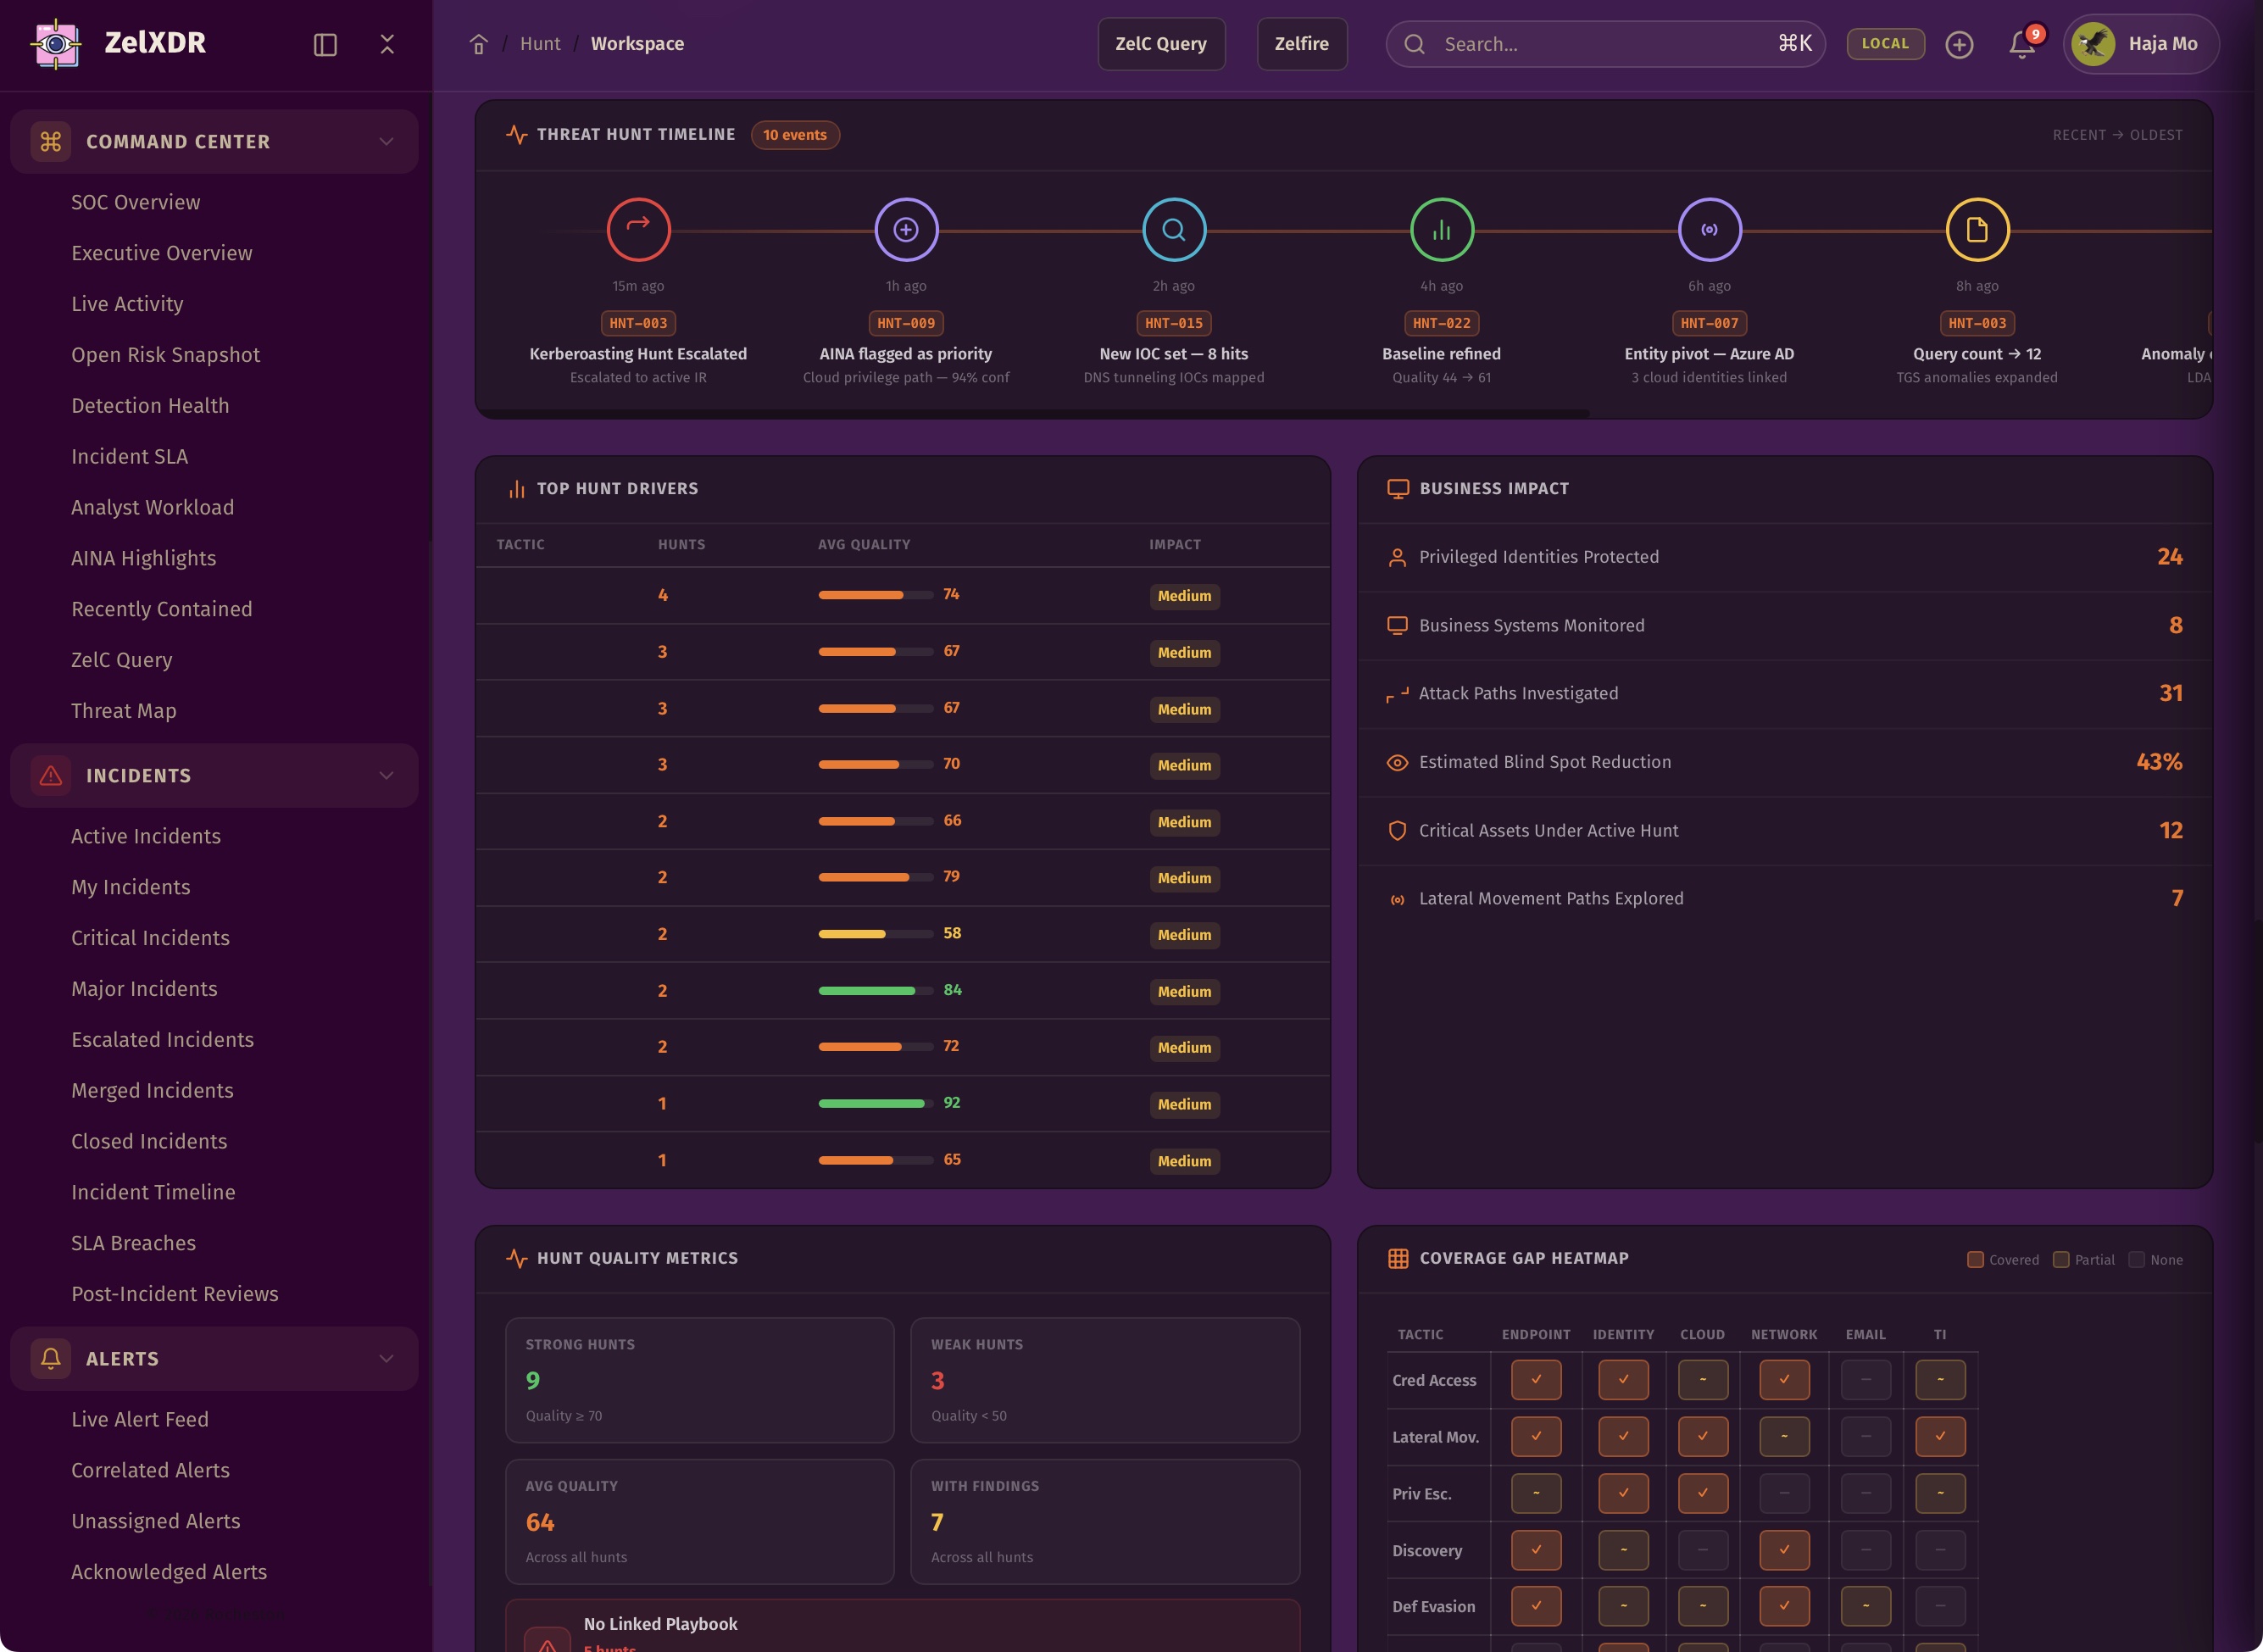
Yes. Threat hunting is a major part of ZelXDR. The platform includes hunt workspaces, query building, saved hunts, hunt templates, IOC search, entity pivoting, historical search, baselines, anomalies, hunt results, and hunt notes so that hunting is operational, repeatable, and evidence-driven.
The Threat Hunt Workspace is the place where analysts and hunters run proactive investigations, explore hypotheses, pivot through evidence, evaluate anomalies, and escalate meaningful findings. It is built to support active hunt operations rather than passive data viewing.
Query Builder is the interactive hunt-query environment inside ZelXDR. It supports building, editing, saving, sharing, and executing hunt logic so analysts can move from questions to structured investigative searches. It is meant to function as a real operational query lab.
Saved Hunts are reusable hunt definitions and investigative workflows that analysts can store for later execution, sharing, or refinement. They help teams turn good hunt logic into repeatable operational knowledge instead of reinventing searches every time.
Hunt Templates are reusable blueprints for threat hunting workflows. They can include hypothesis structures, query blocks, pivot ideas, baseline checks, IOC paths, and escalation logic so that teams can standardize effective hunts across the organization.
IOC Search is the part of ZelXDR that searches indicators such as IPs, domains, hashes, URLs, emails, and related artifacts across internal telemetry and linked intelligence context. It helps determine whether indicators are benign, suspicious, active, stale, or connected to broader threat activity.
Entity Pivot Search is the relationship-based investigative experience where users pivot from one entity to others. It can connect users, endpoints, IPs, domains, alerts, cases, incidents, sessions, and other related objects to help analysts understand relationship chains and hidden context.
Historical Search lets users investigate older telemetry, recurring patterns, archived events, and long-range behavior. It helps analysts uncover prior activity, recurring abuse, older weak signals, and long-tail relationships that matter in current investigations.
Baselines are expected-behavior models used to understand normality for users, endpoints, service accounts, cloud resources, and other objects. These baselines support anomaly detection, hunt logic, and operational context by showing what is normal and where meaningful deviation begins.
Anomalies are meaningful deviations from expected behavior identified inside the platform. They can come from baseline deviation, peer-group difference, rare events, sequence breaks, volume spikes, identity anomalies, cloud anomalies, or other abnormal patterns.
Hunt Results are structured findings that come from proactive investigations. They can include evidence-backed results, recurring patterns, linked entities, linked IOCs, baseline deviations, and escalation candidates that move hunts into incidents, cases, detections, or reports.
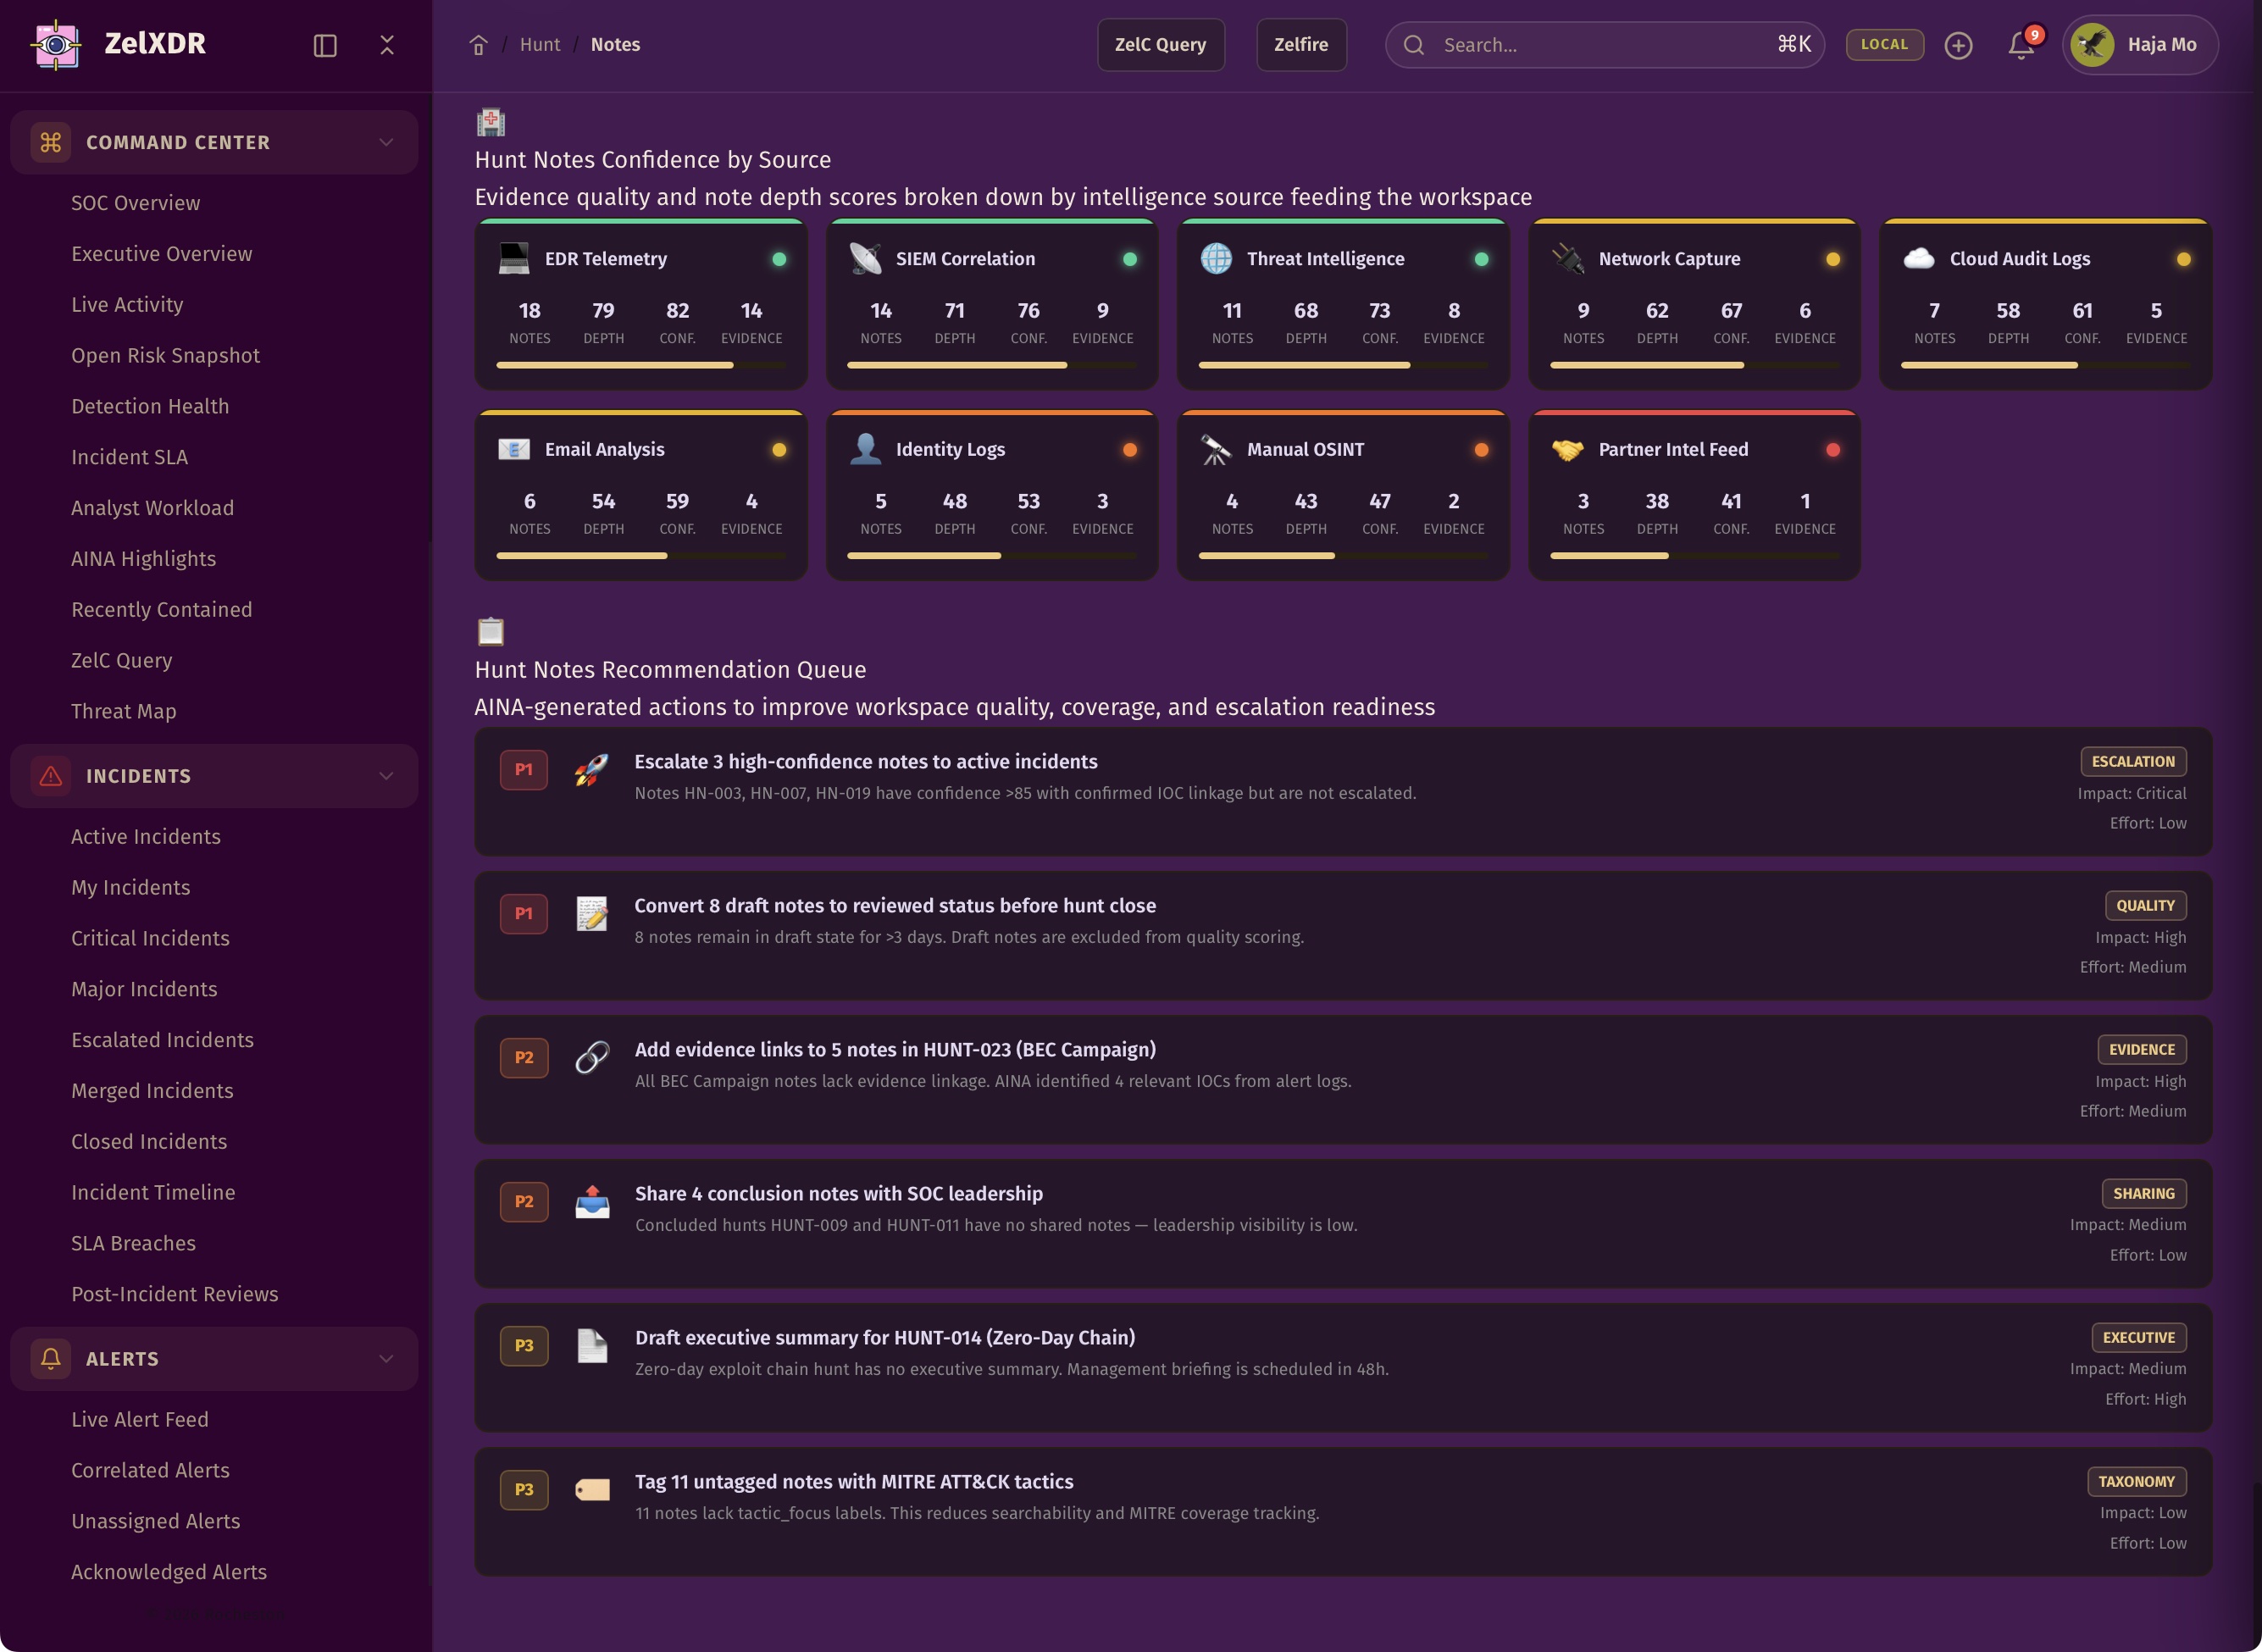
Hunt Notes are structured investigation notes tied to hunts, evidence, entities, indicators, results, and escalations. They support analyst writing, knowledge capture, AI-assisted drafting, evidence-backed note organization, and conversion into executive or operational summaries.
Yes. The Hunt Notes experience is meant to behave like a real investigation writing workspace with note editing, save, delete, share, pinning, linkage to evidence, and AI writing support. The goal is to turn analyst note-taking into a first-class operational capability.
ZelXDR supports detection rules, correlation rules, behavioral detections, analytics rules, and scheduled rules. It also supports related tuning, QA, exceptions, change tracking, MITRE mapping, severity logic, and threat scoring so detections can be engineered and governed as a living system.
Detection Rules are the core logic units that identify suspicious conditions based on platform data. They are designed to be manageable, tunable, explainable, and connected to MITRE coverage, playbooks, scoring, and operational outcomes.
Correlation Rules are logic units that connect related signals across domains such as endpoint, identity, cloud, network, and email. Their purpose is to turn isolated events into higher-confidence narratives and reduce the analyst burden of connecting evidence manually.
Behavioral Detections focus on suspicious patterns rather than static signatures. They use user behavior, entity patterns, peer groups, seasonality, and deviation logic to identify potentially risky activity that would not be captured by simple pattern matching alone.
Analytics Rules are metric-driven detection components that use thresholds, ratios, rare event logic, entropy, drift, and scoring logic to identify meaningful patterns. They provide more mathematically driven detection behavior where appropriate.
Scheduled Rules are time-based detection and analytic jobs that run on defined cadences. They help surface issues that are best identified through periodic review rather than purely event-triggered logic.
Threat Scoring Logic is the part of ZelXDR that weights different signals and context factors to determine which threats deserve more attention. It may consider confidence, asset criticality, identity sensitivity, business impact, threat intelligence, and related evidence.
Severity Mapping determines how platform logic translates findings into severity bands such as low, medium, high, or critical. It helps the platform assign operational urgency based on a structured set of logic and contextual inputs.
MITRE Mappings connects detections, hunts, results, and related security logic to MITRE ATT&CK tactics, techniques, and sub-techniques. This gives teams a structured way to understand detection coverage and operational alignment against attacker behavior.
Detection Packs are reusable bundles of security logic, mappings, playbooks, scoring settings, and operational pieces that can be grouped together for structured deployment and reuse. They help teams scale detection engineering with more consistency.
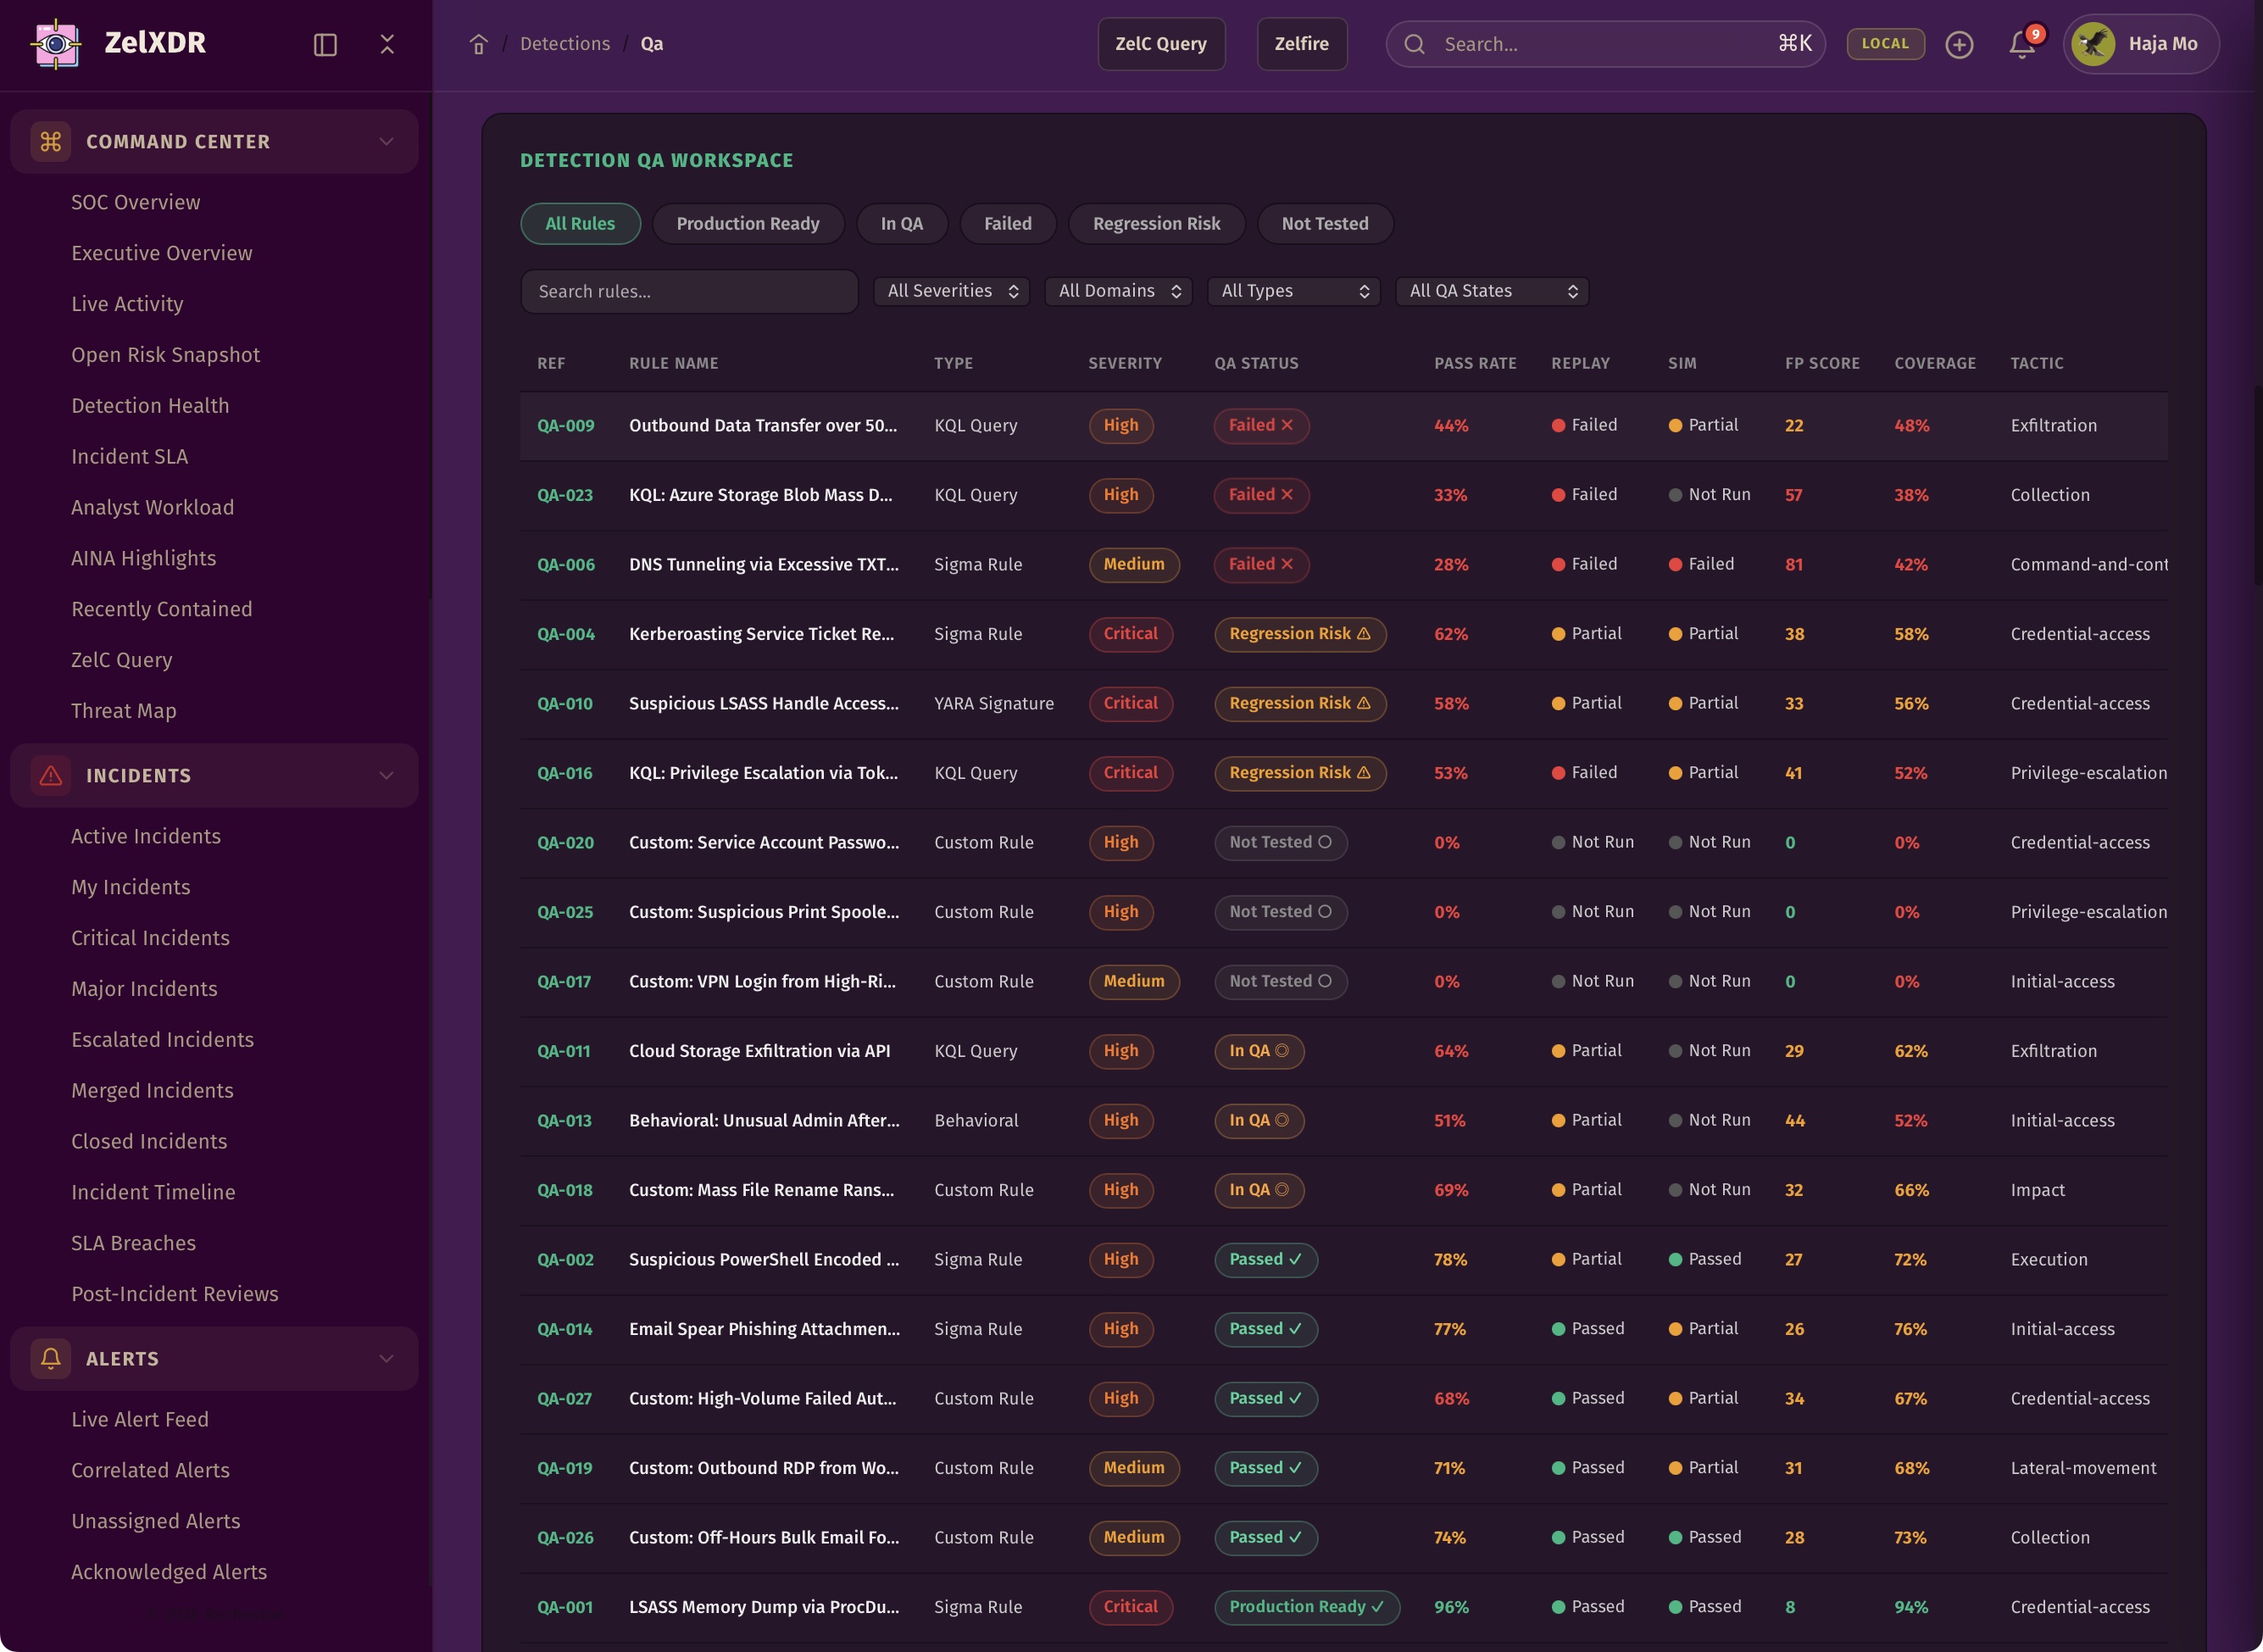
Detection QA is the validation layer for detections. It is designed to support testing, replay, simulation, regression review, and quality evaluation so teams can verify whether detections are production-ready and trustworthy.
Rule Tuning is the process of refining detection behavior so that rules become more precise, less noisy, and more operationally valuable. ZelXDR treats tuning as an ongoing engineering process rather than a one-time edit.
Rule Exceptions are governed waivers, suppressions, allowlists, maintenance windows, or scoped exclusions that help teams reduce justified noise without silently creating blind spots. ZelXDR treats exceptions as governed objects, not throwaway tweaks.
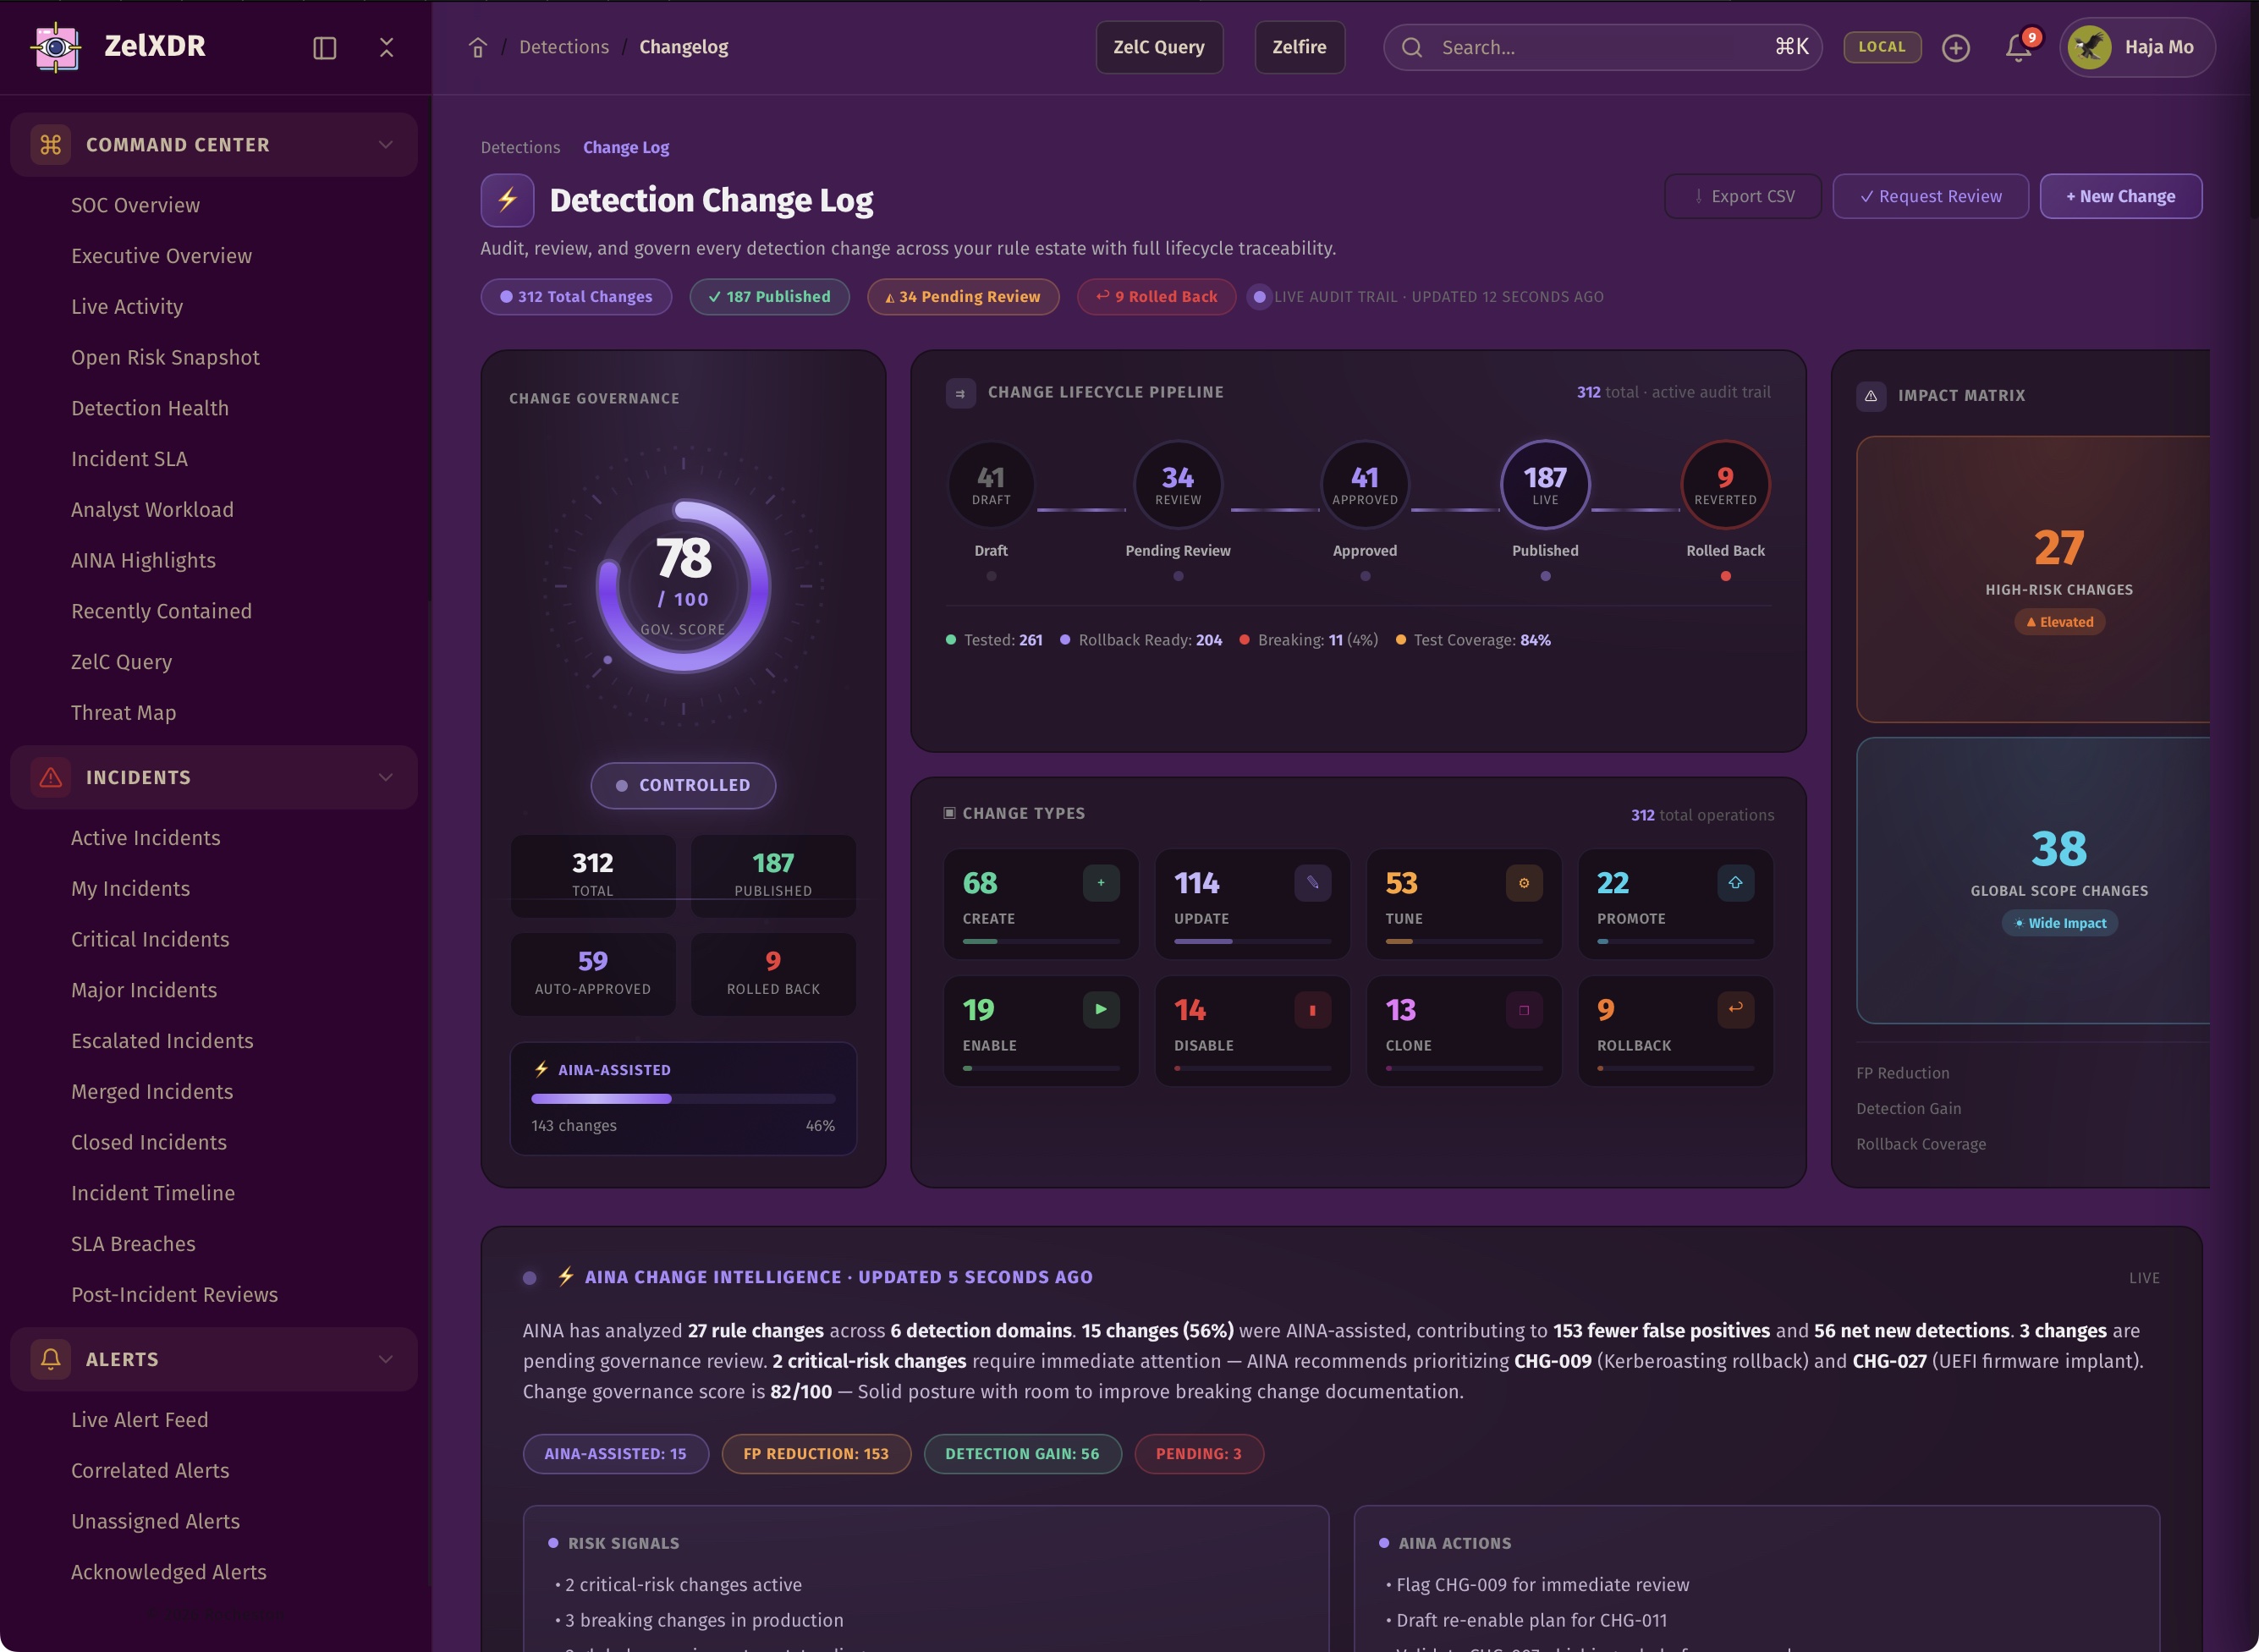
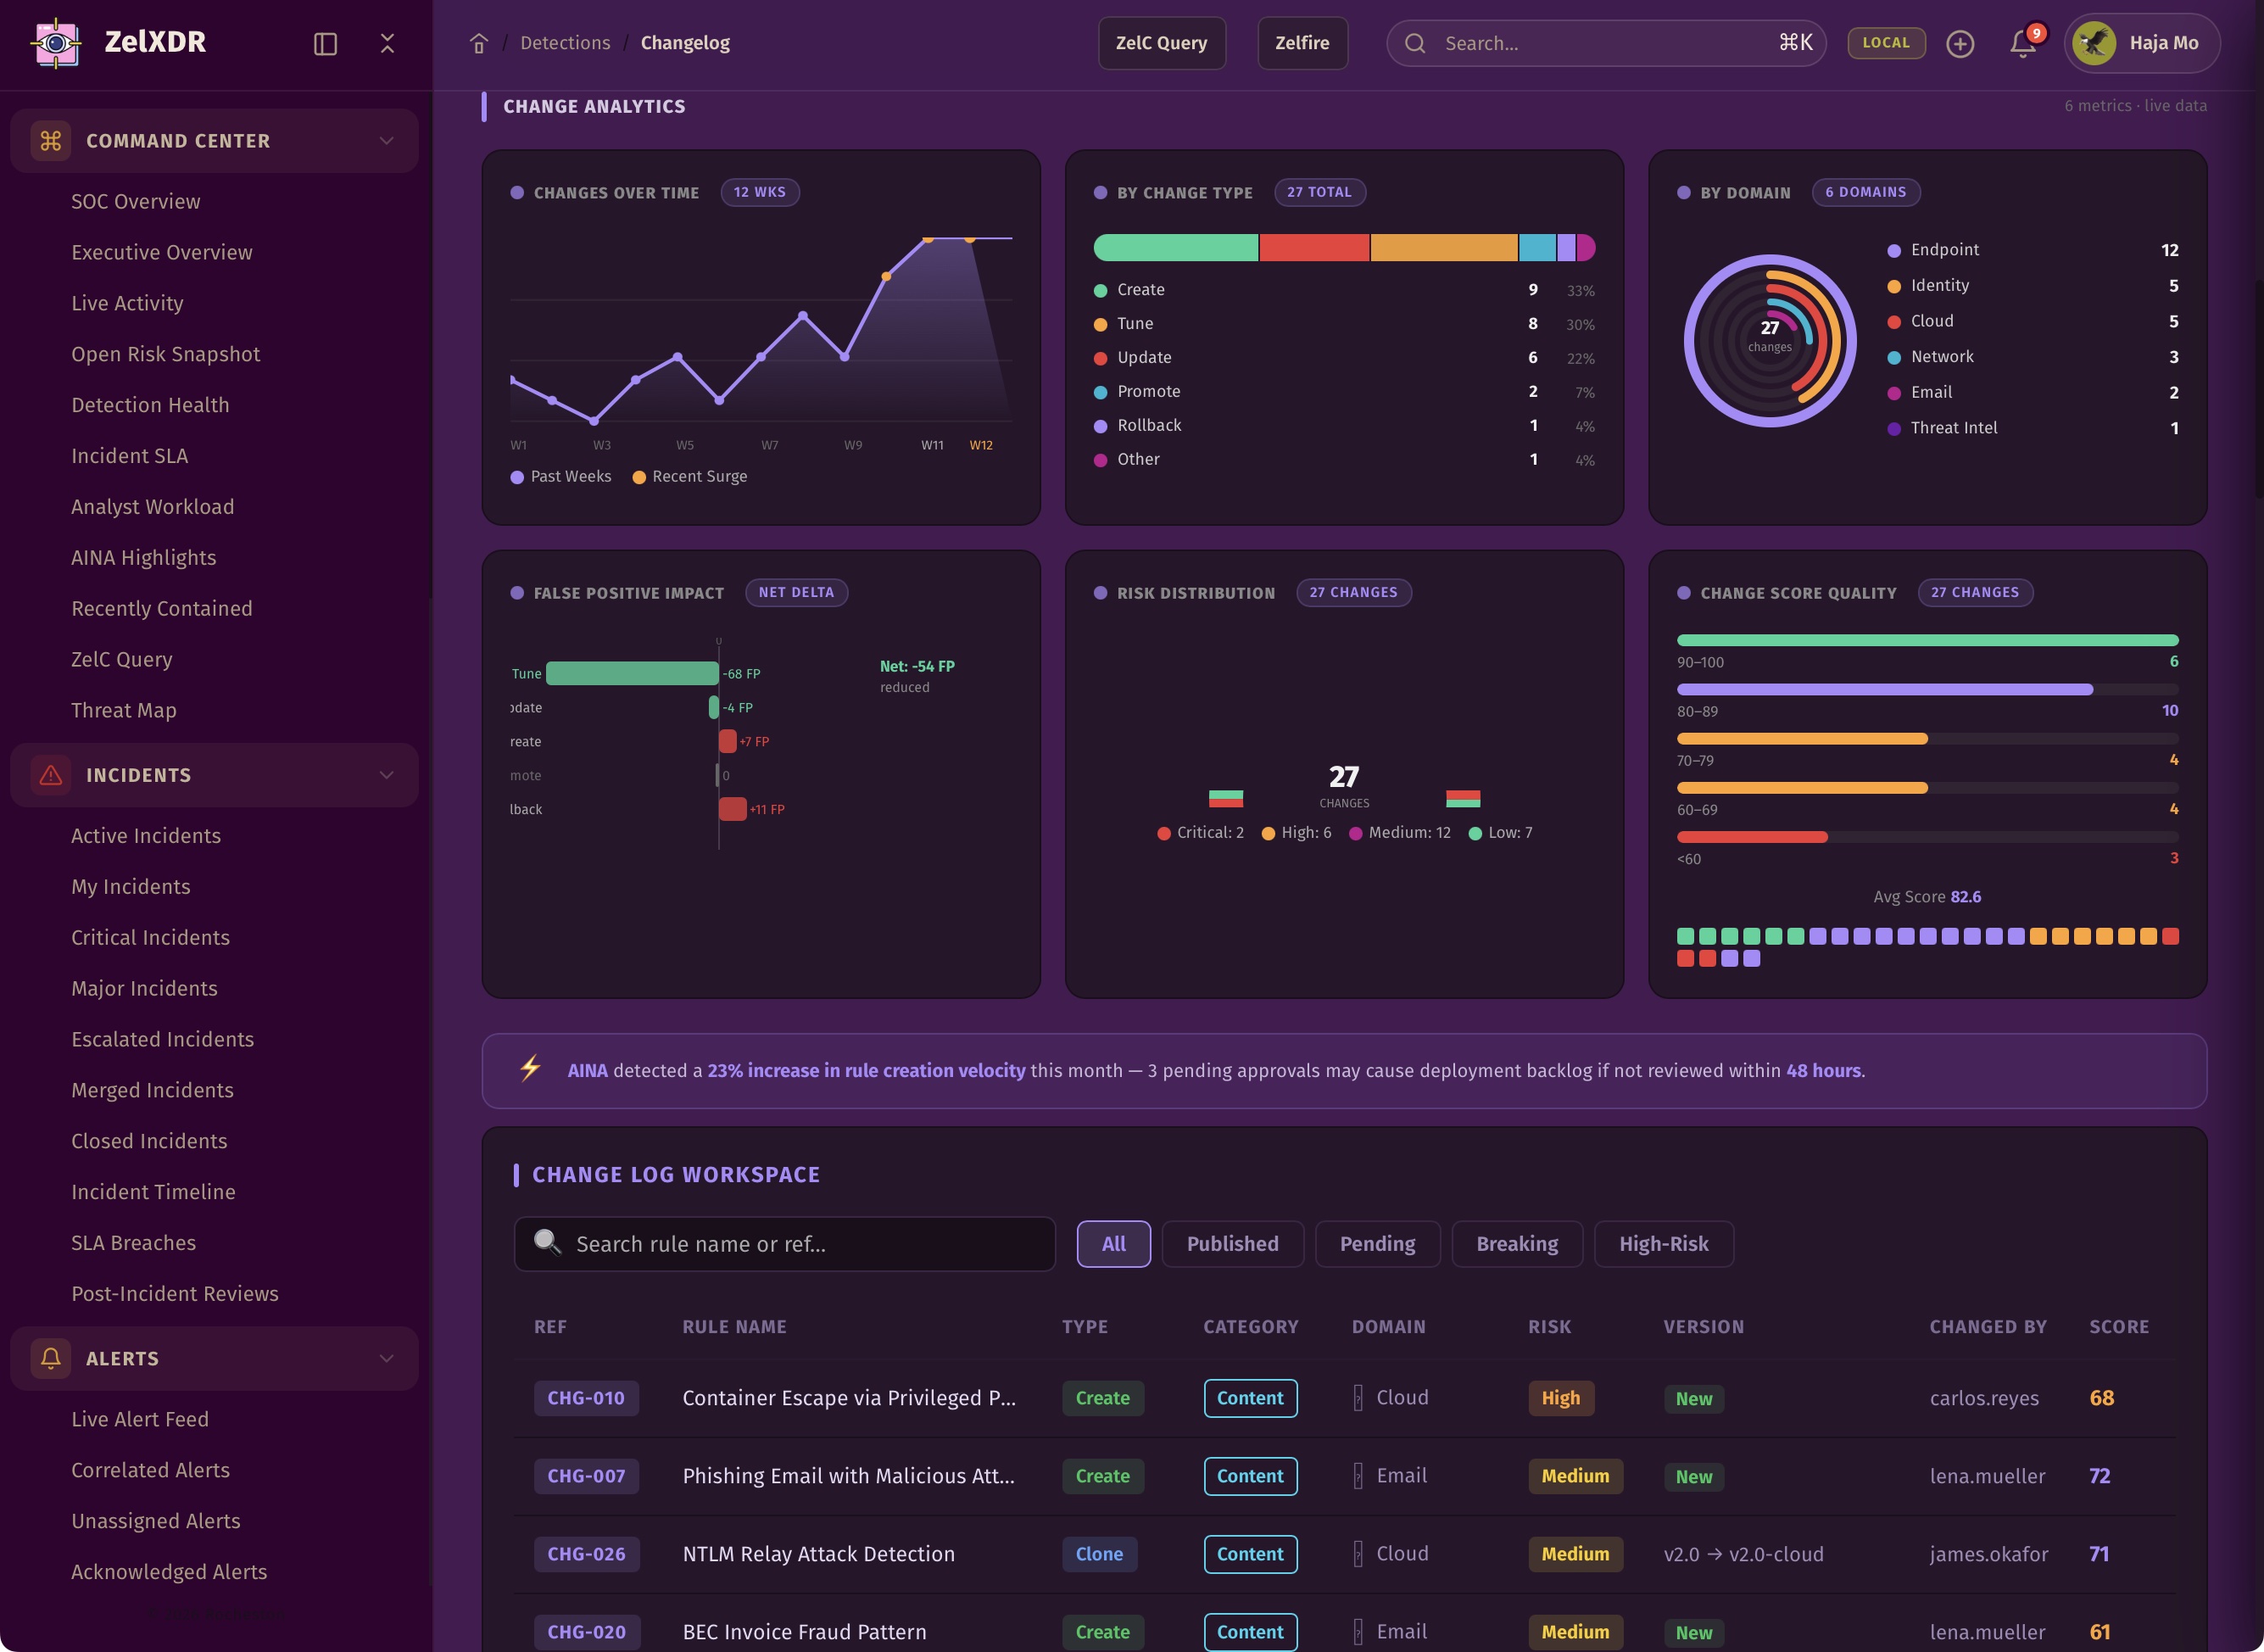
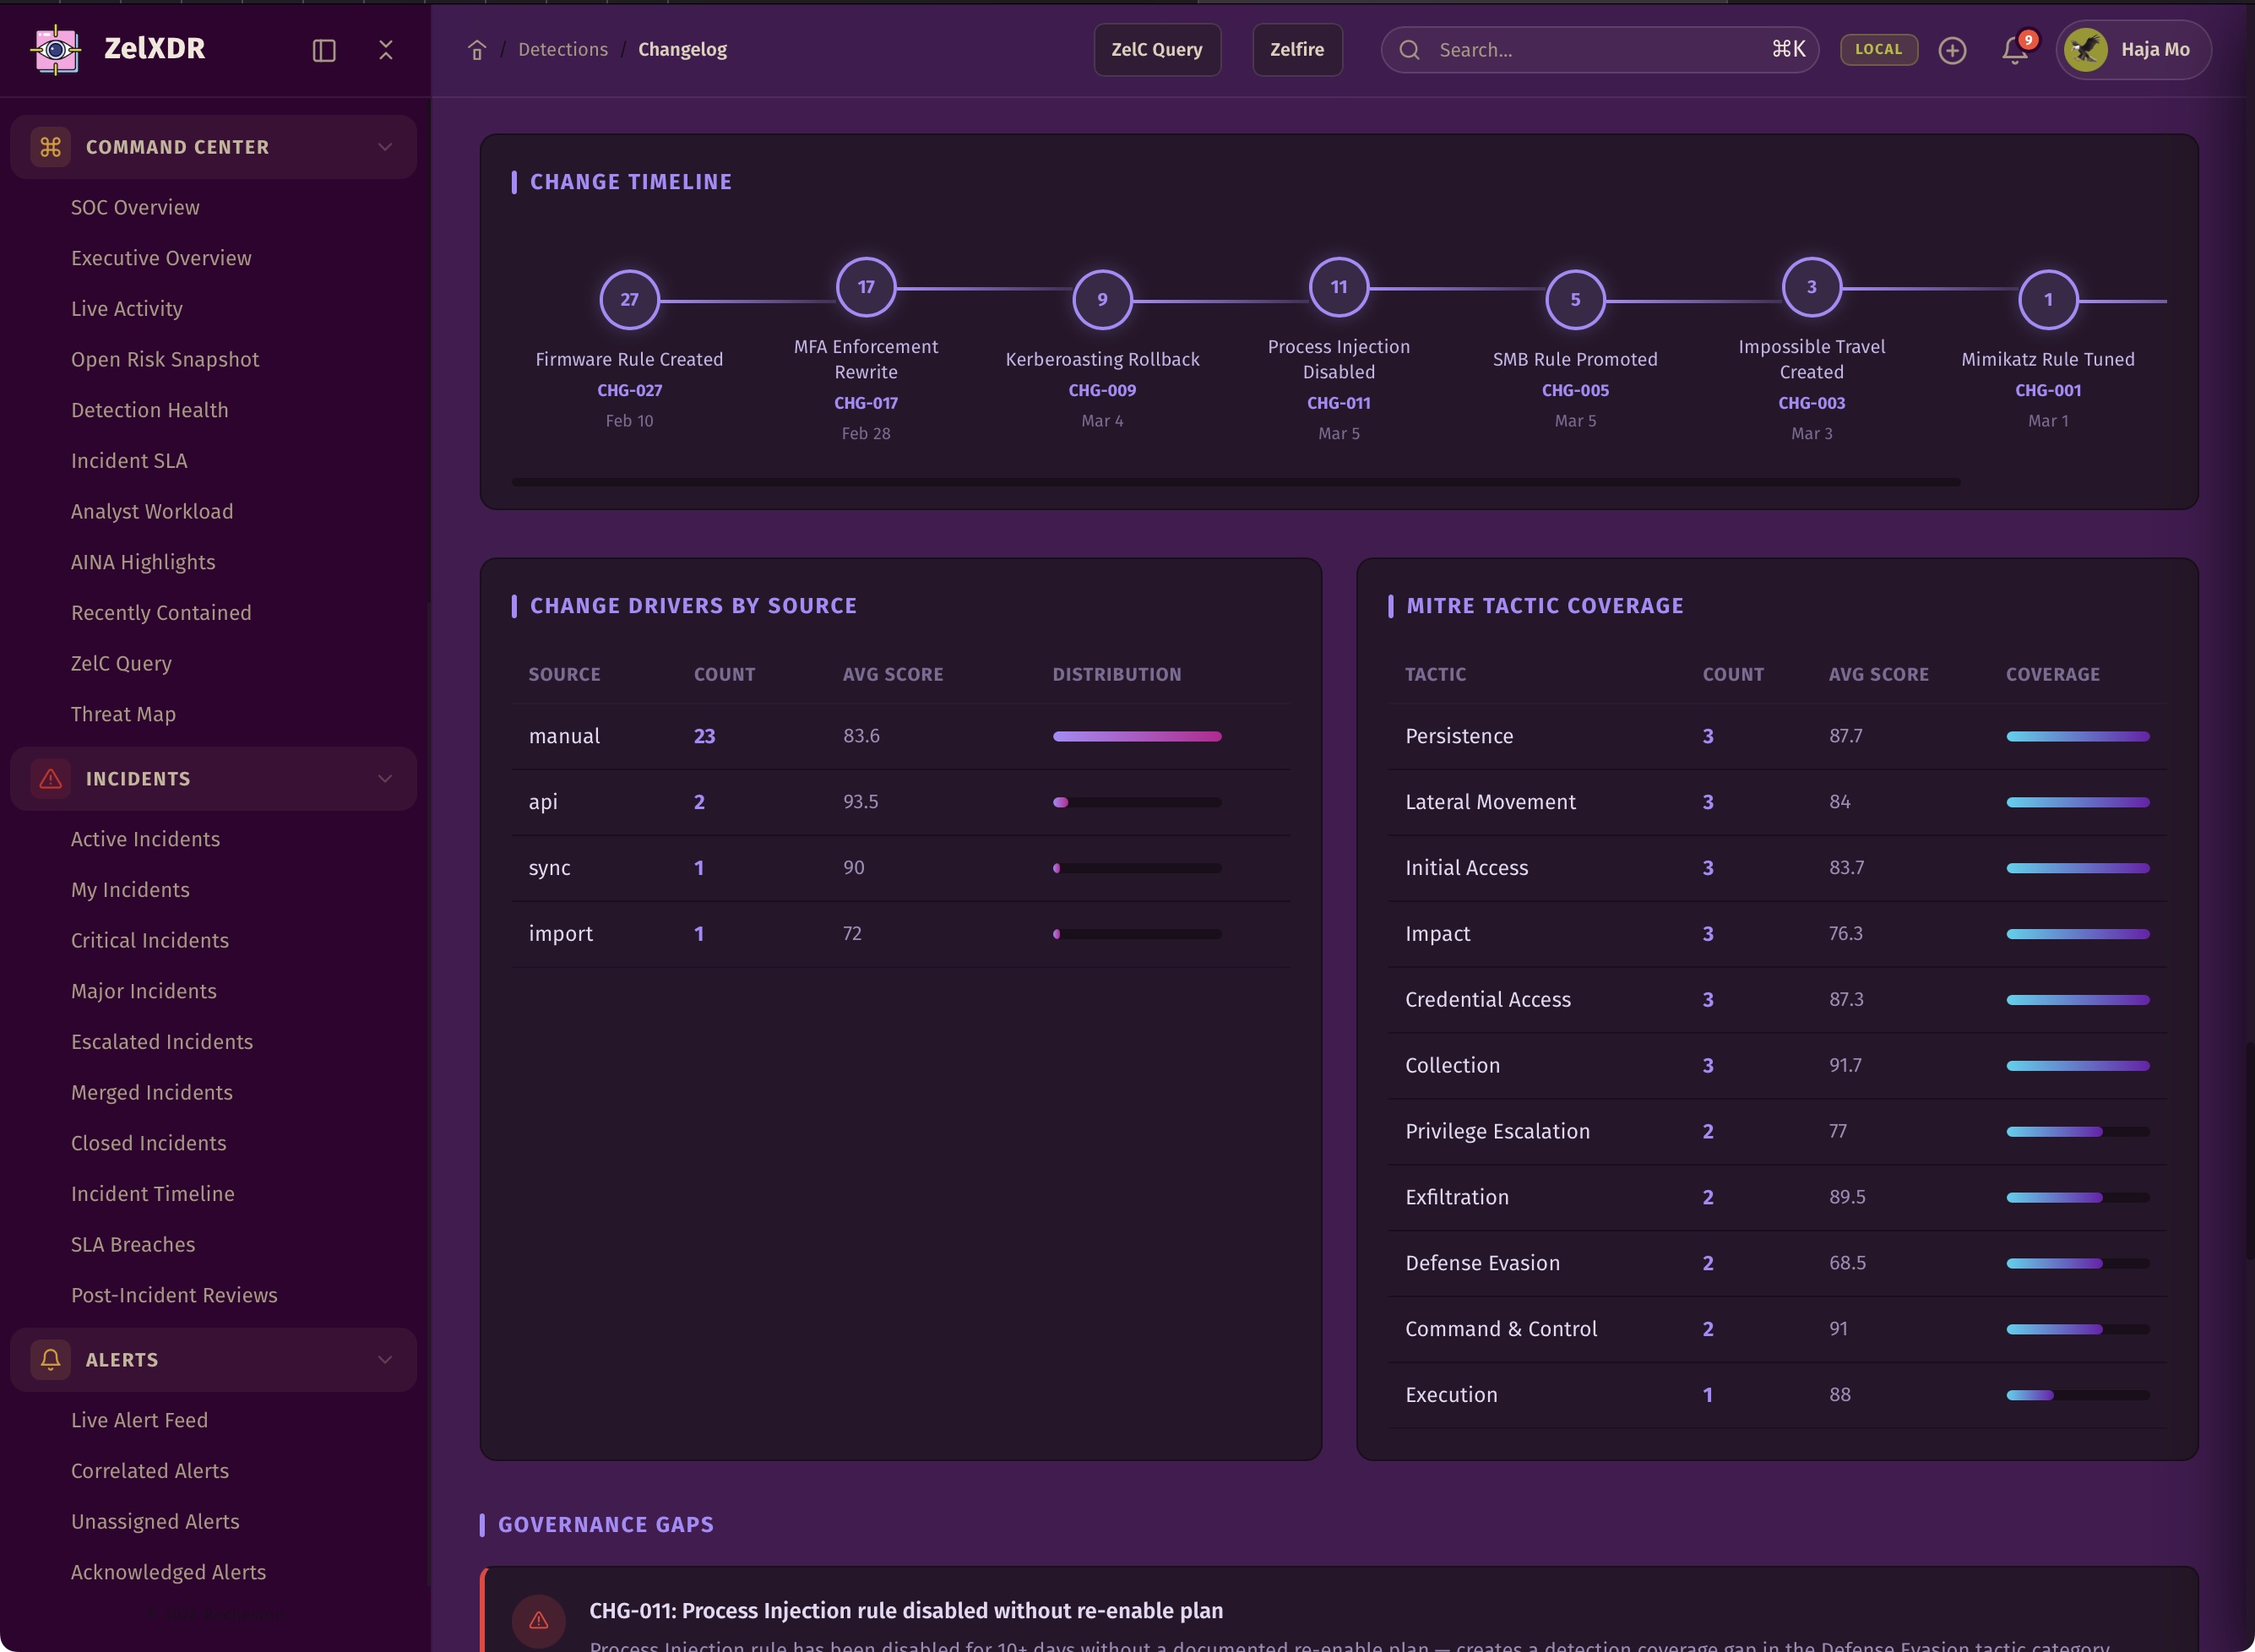
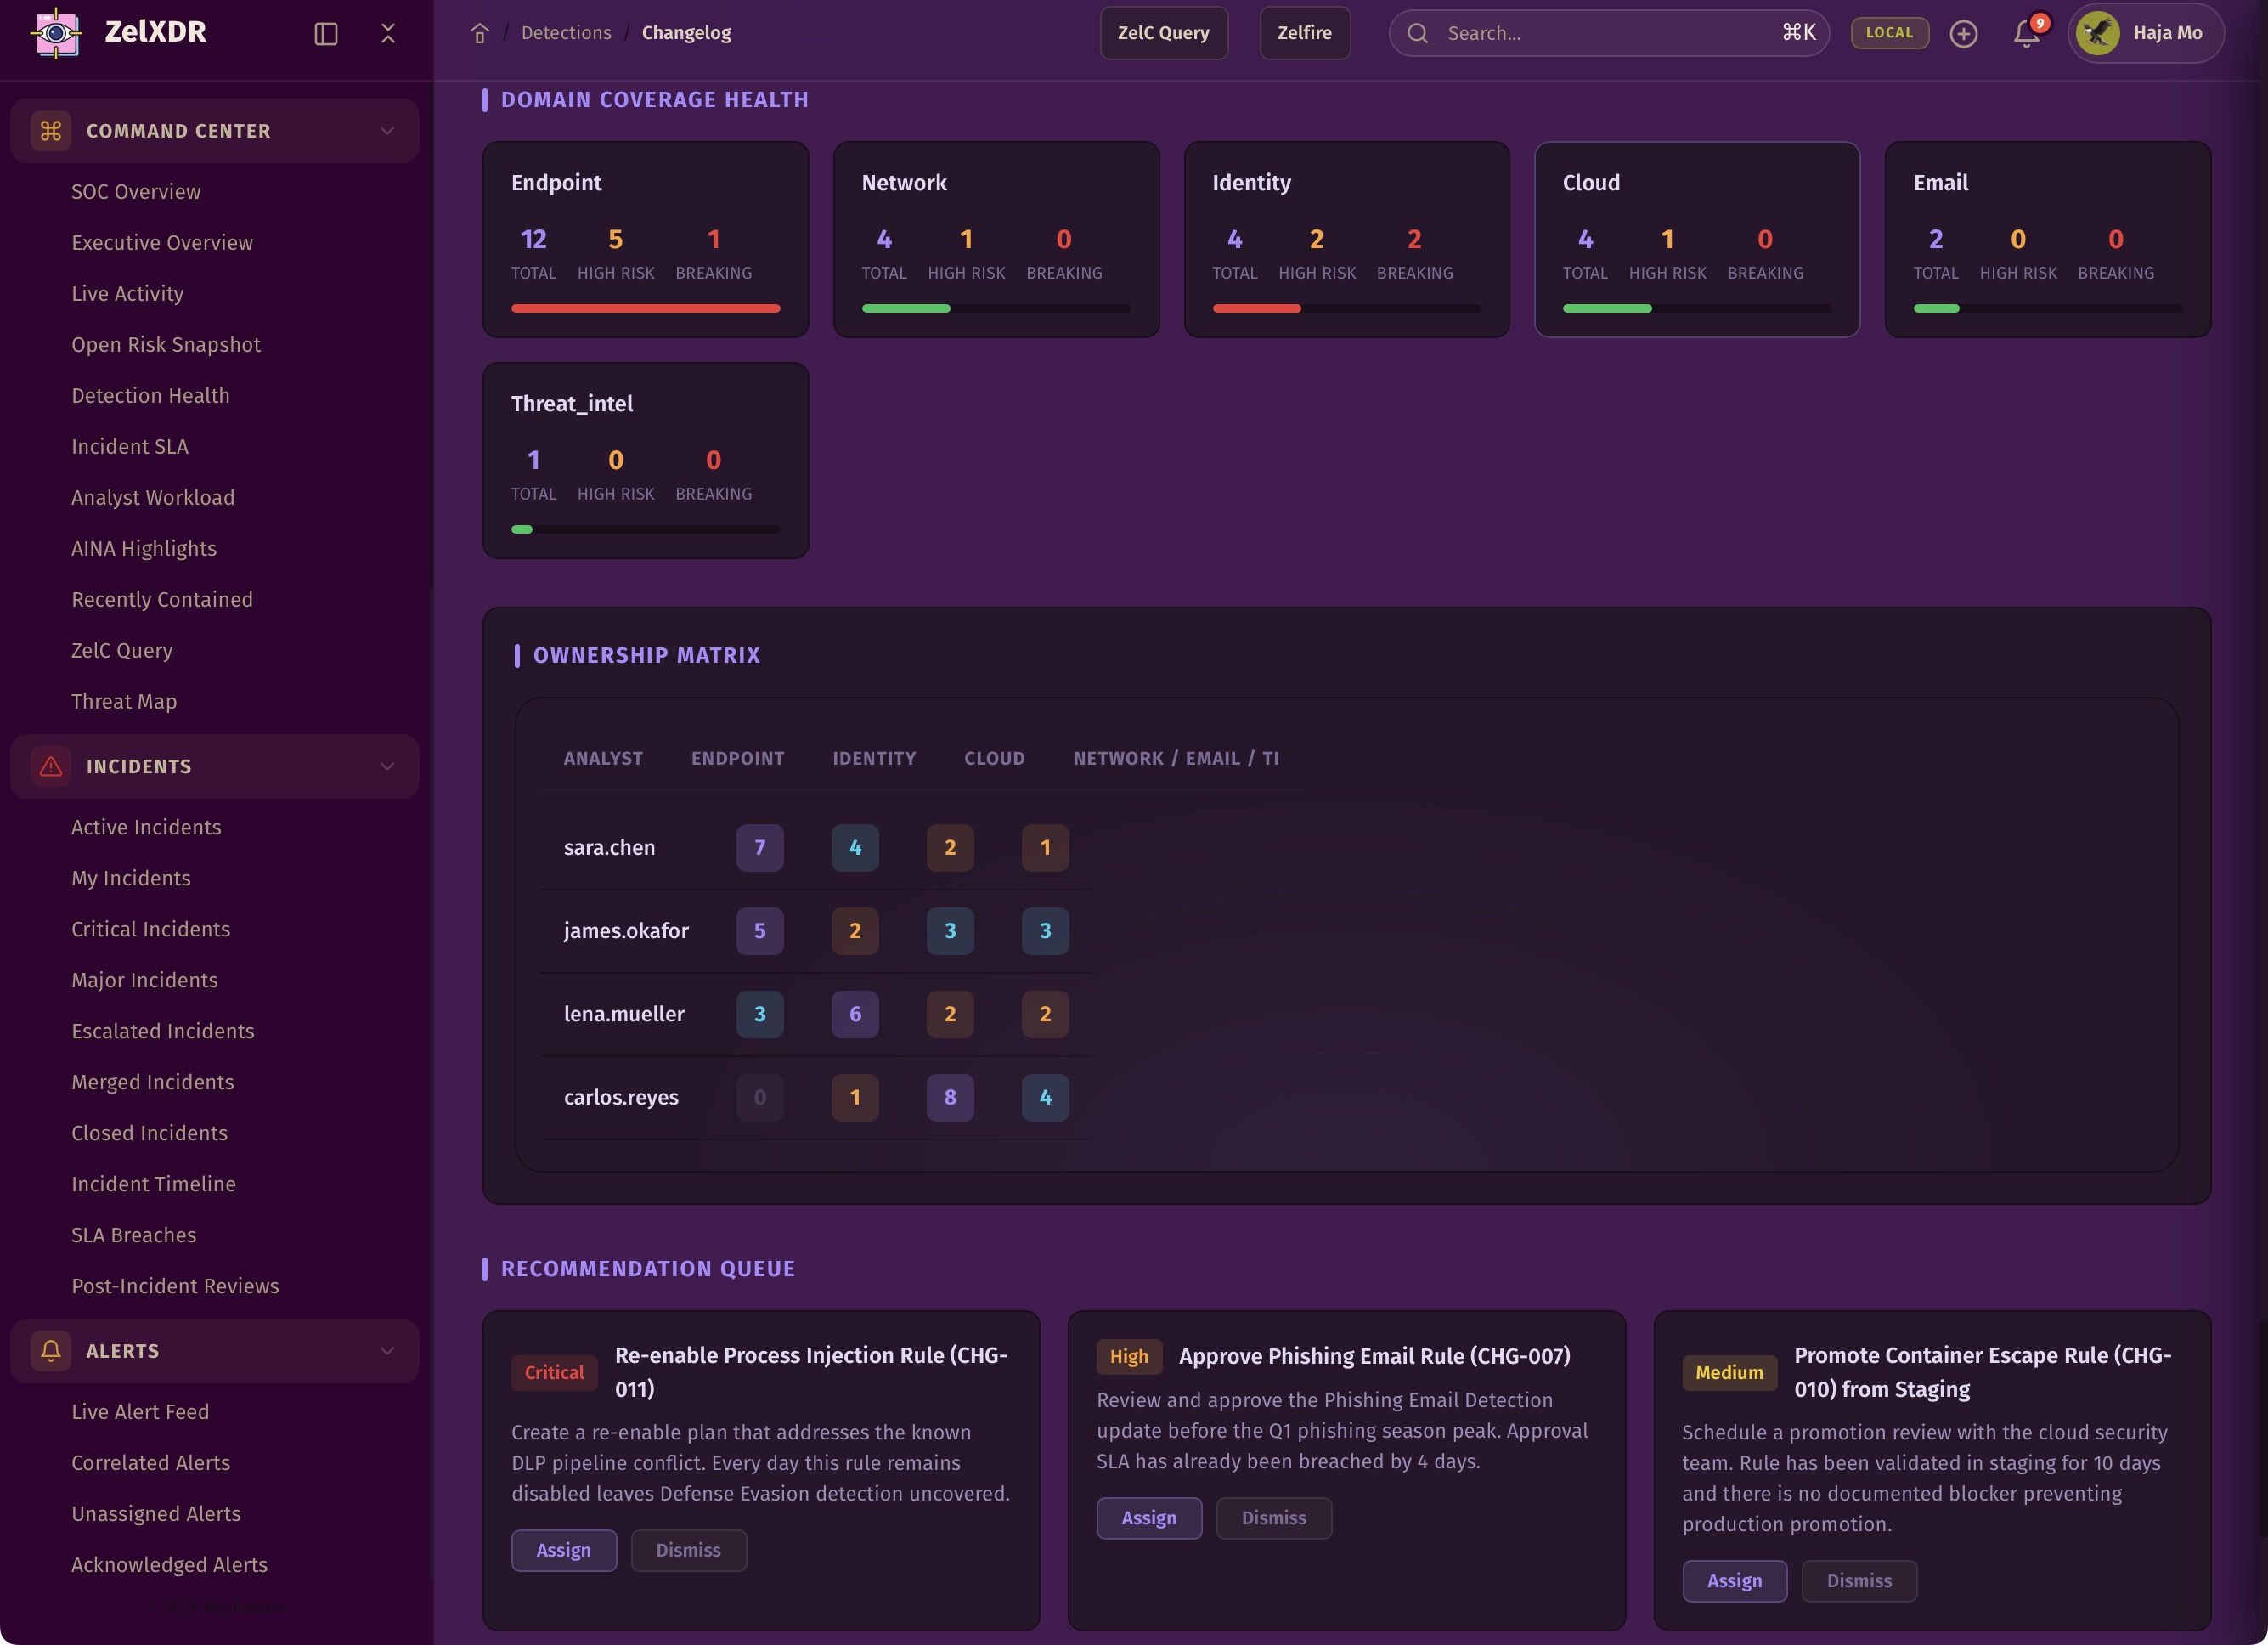
Detection Change Log tracks how detection logic changes over time. It is designed to show who changed what, why it changed, when it changed, and what impact it had on the platform so engineering and governance stay visible.
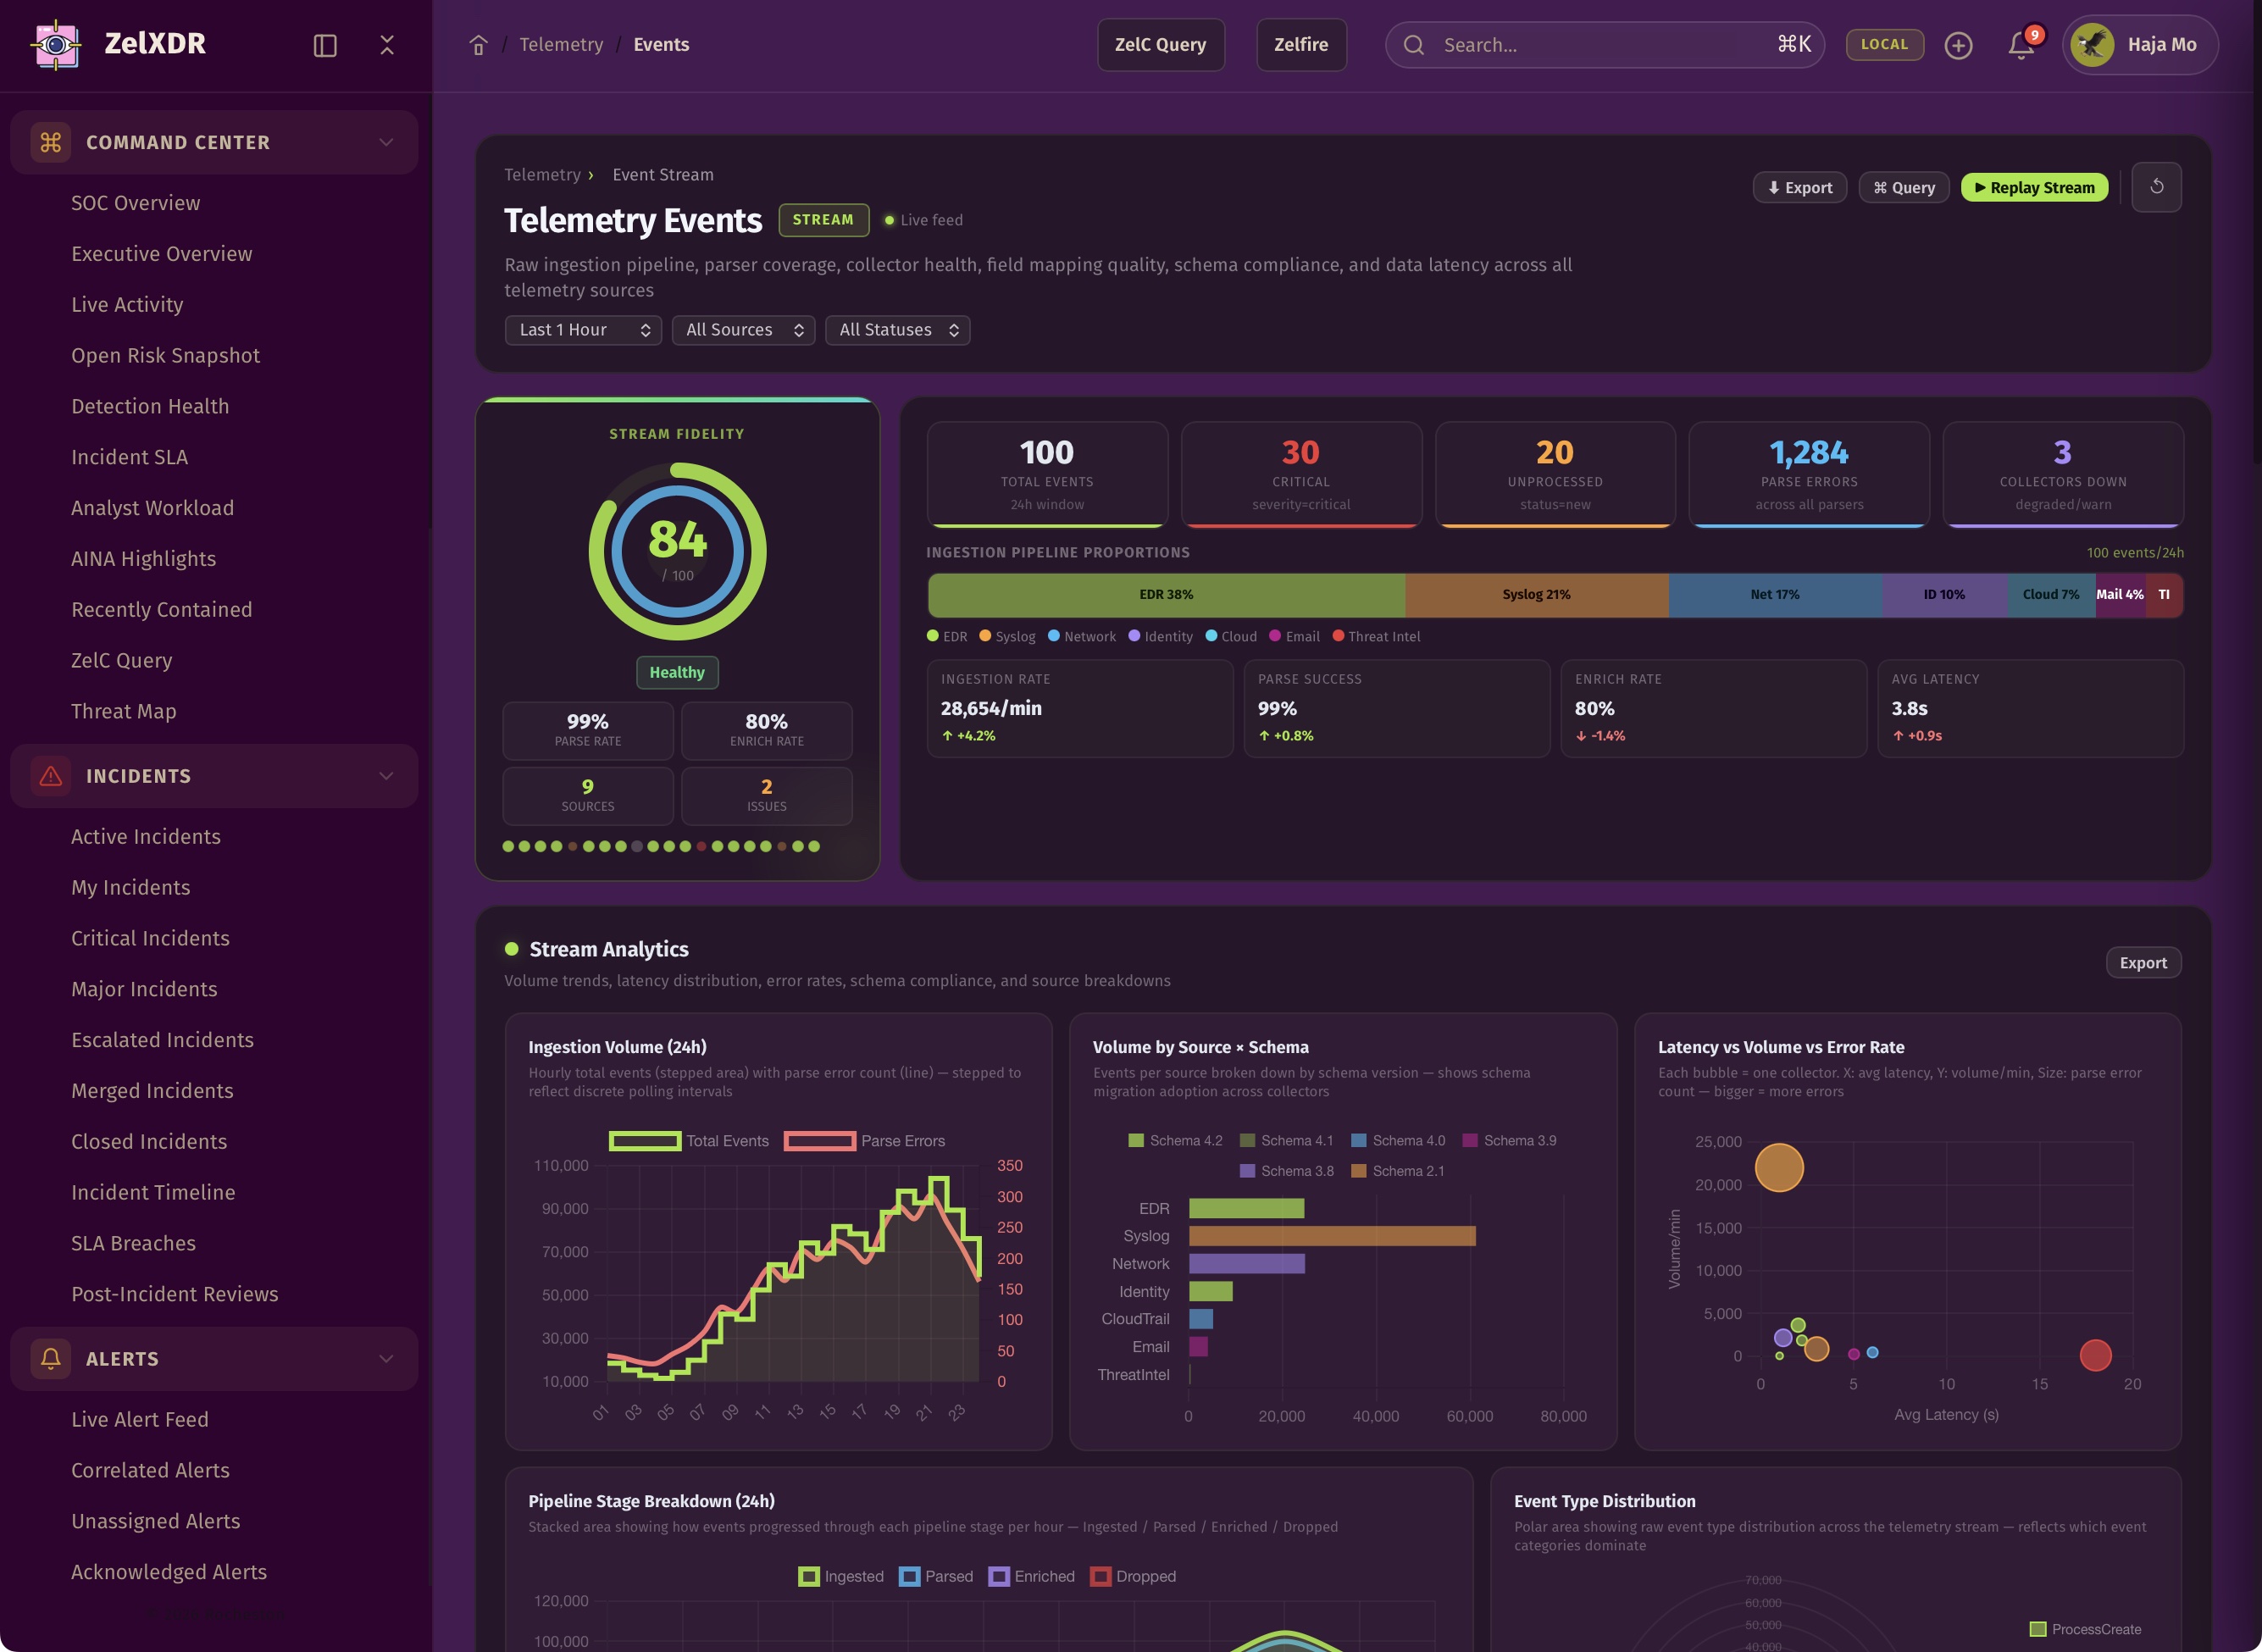
Event Explorer is the unified event investigation workspace for live and historical telemetry. It helps analysts search, inspect, pivot, and reason over events across different security domains without losing context.
Raw Logs are the original source-native telemetry payloads before normalization and enrichment. They are important for troubleshooting parsers, validating source fidelity, inspecting malformed data, and performing deeper forensic analysis when needed.
Normalized Events are canonical event records produced from raw telemetry after parsing and mapping. They allow different source systems to be analyzed in a more consistent, unified way across the platform.
Enriched Events are normalized events with extra context added, such as identity, asset, threat intelligence, correlation, relationship, and business context. They help analysts move faster from observation to understanding.
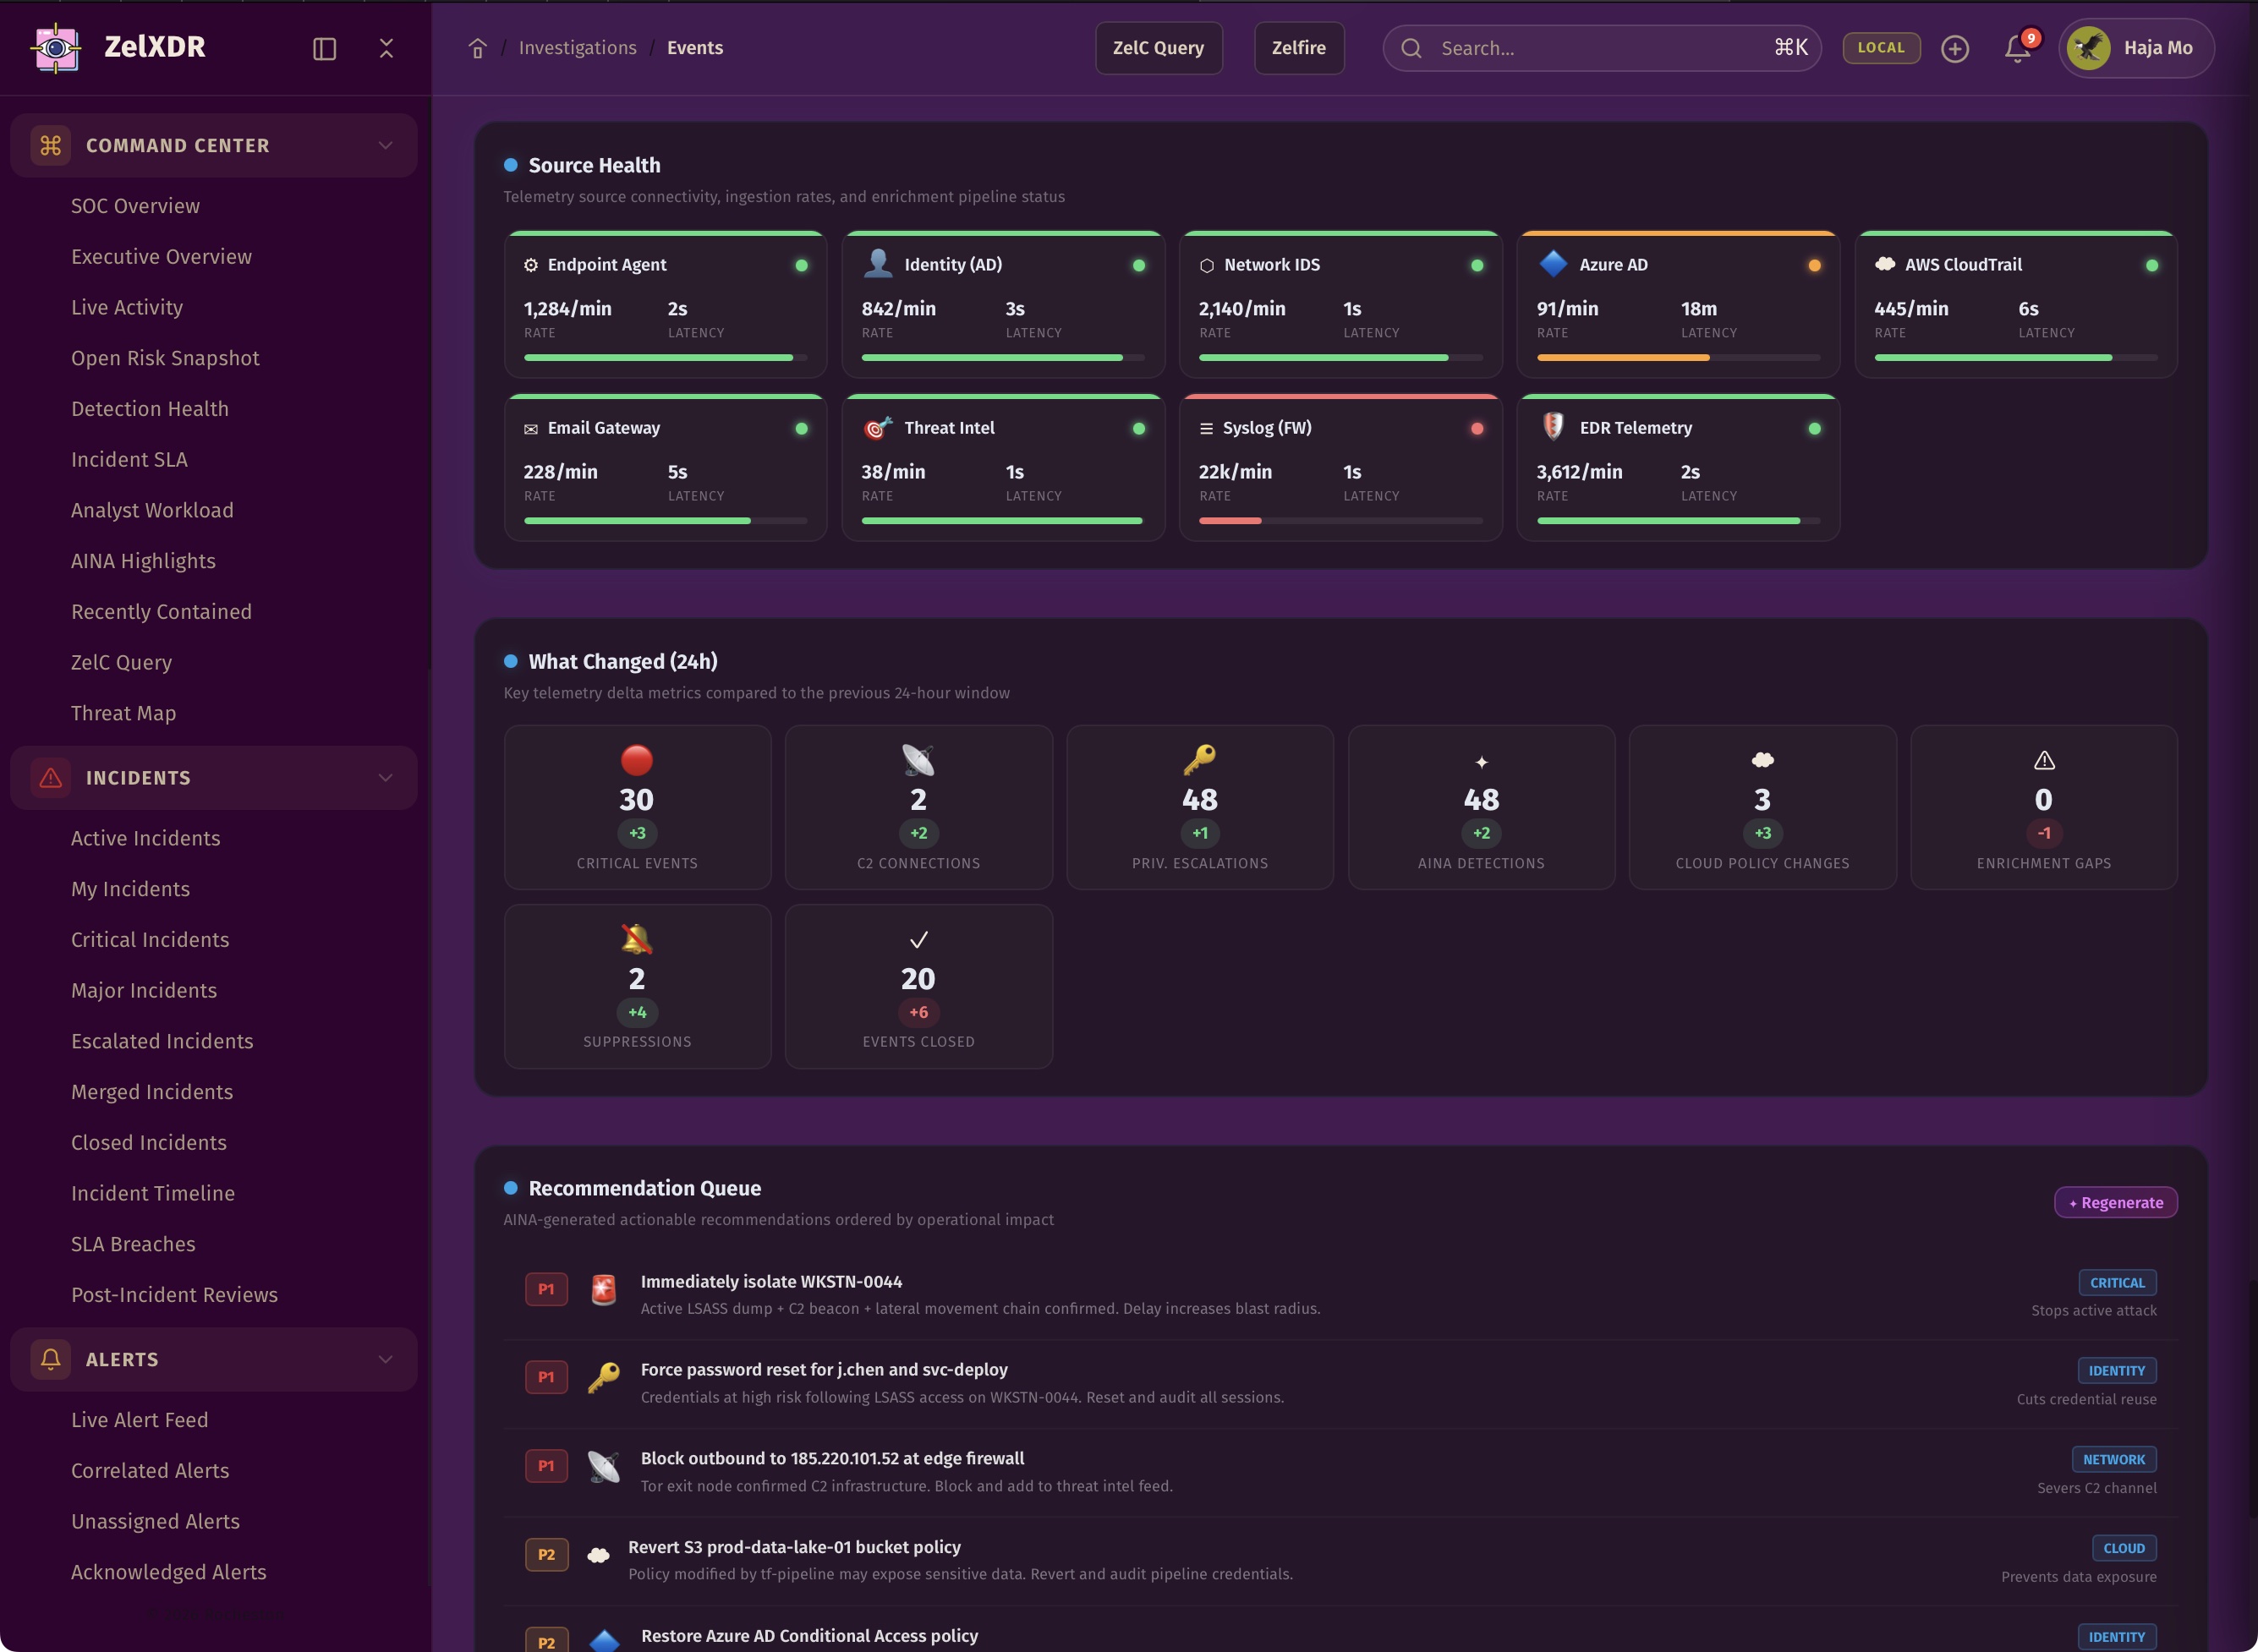
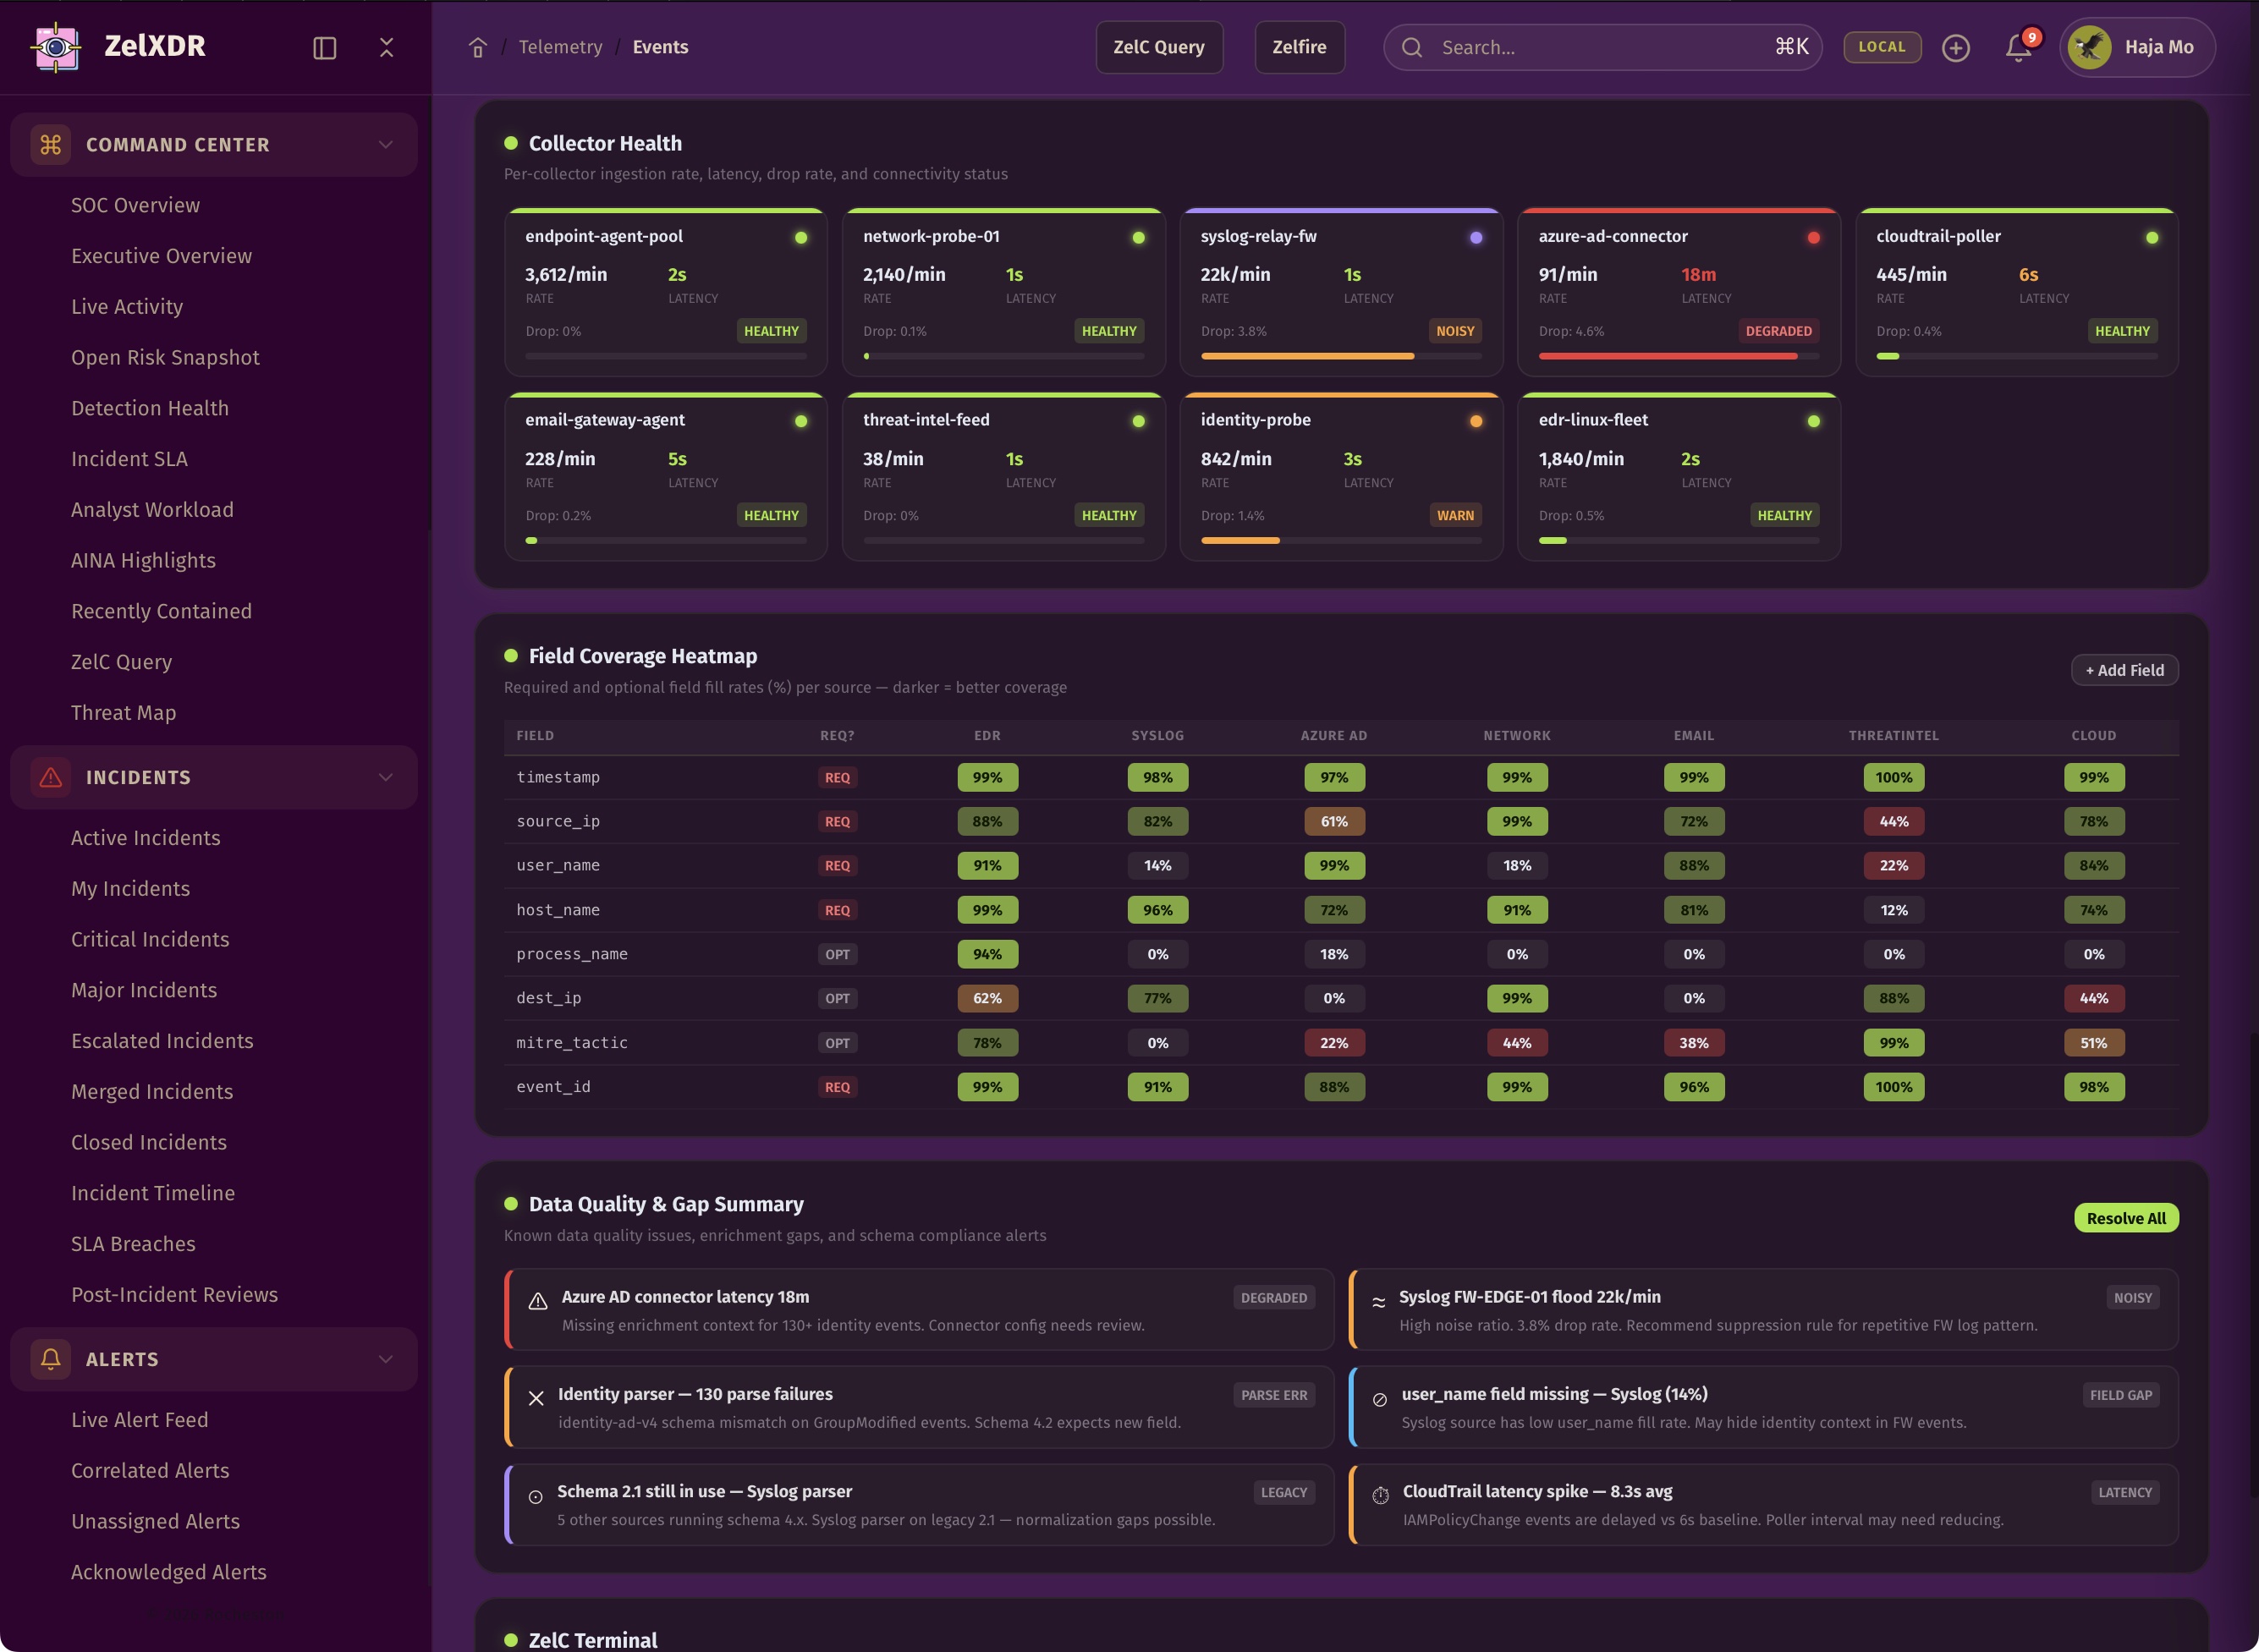
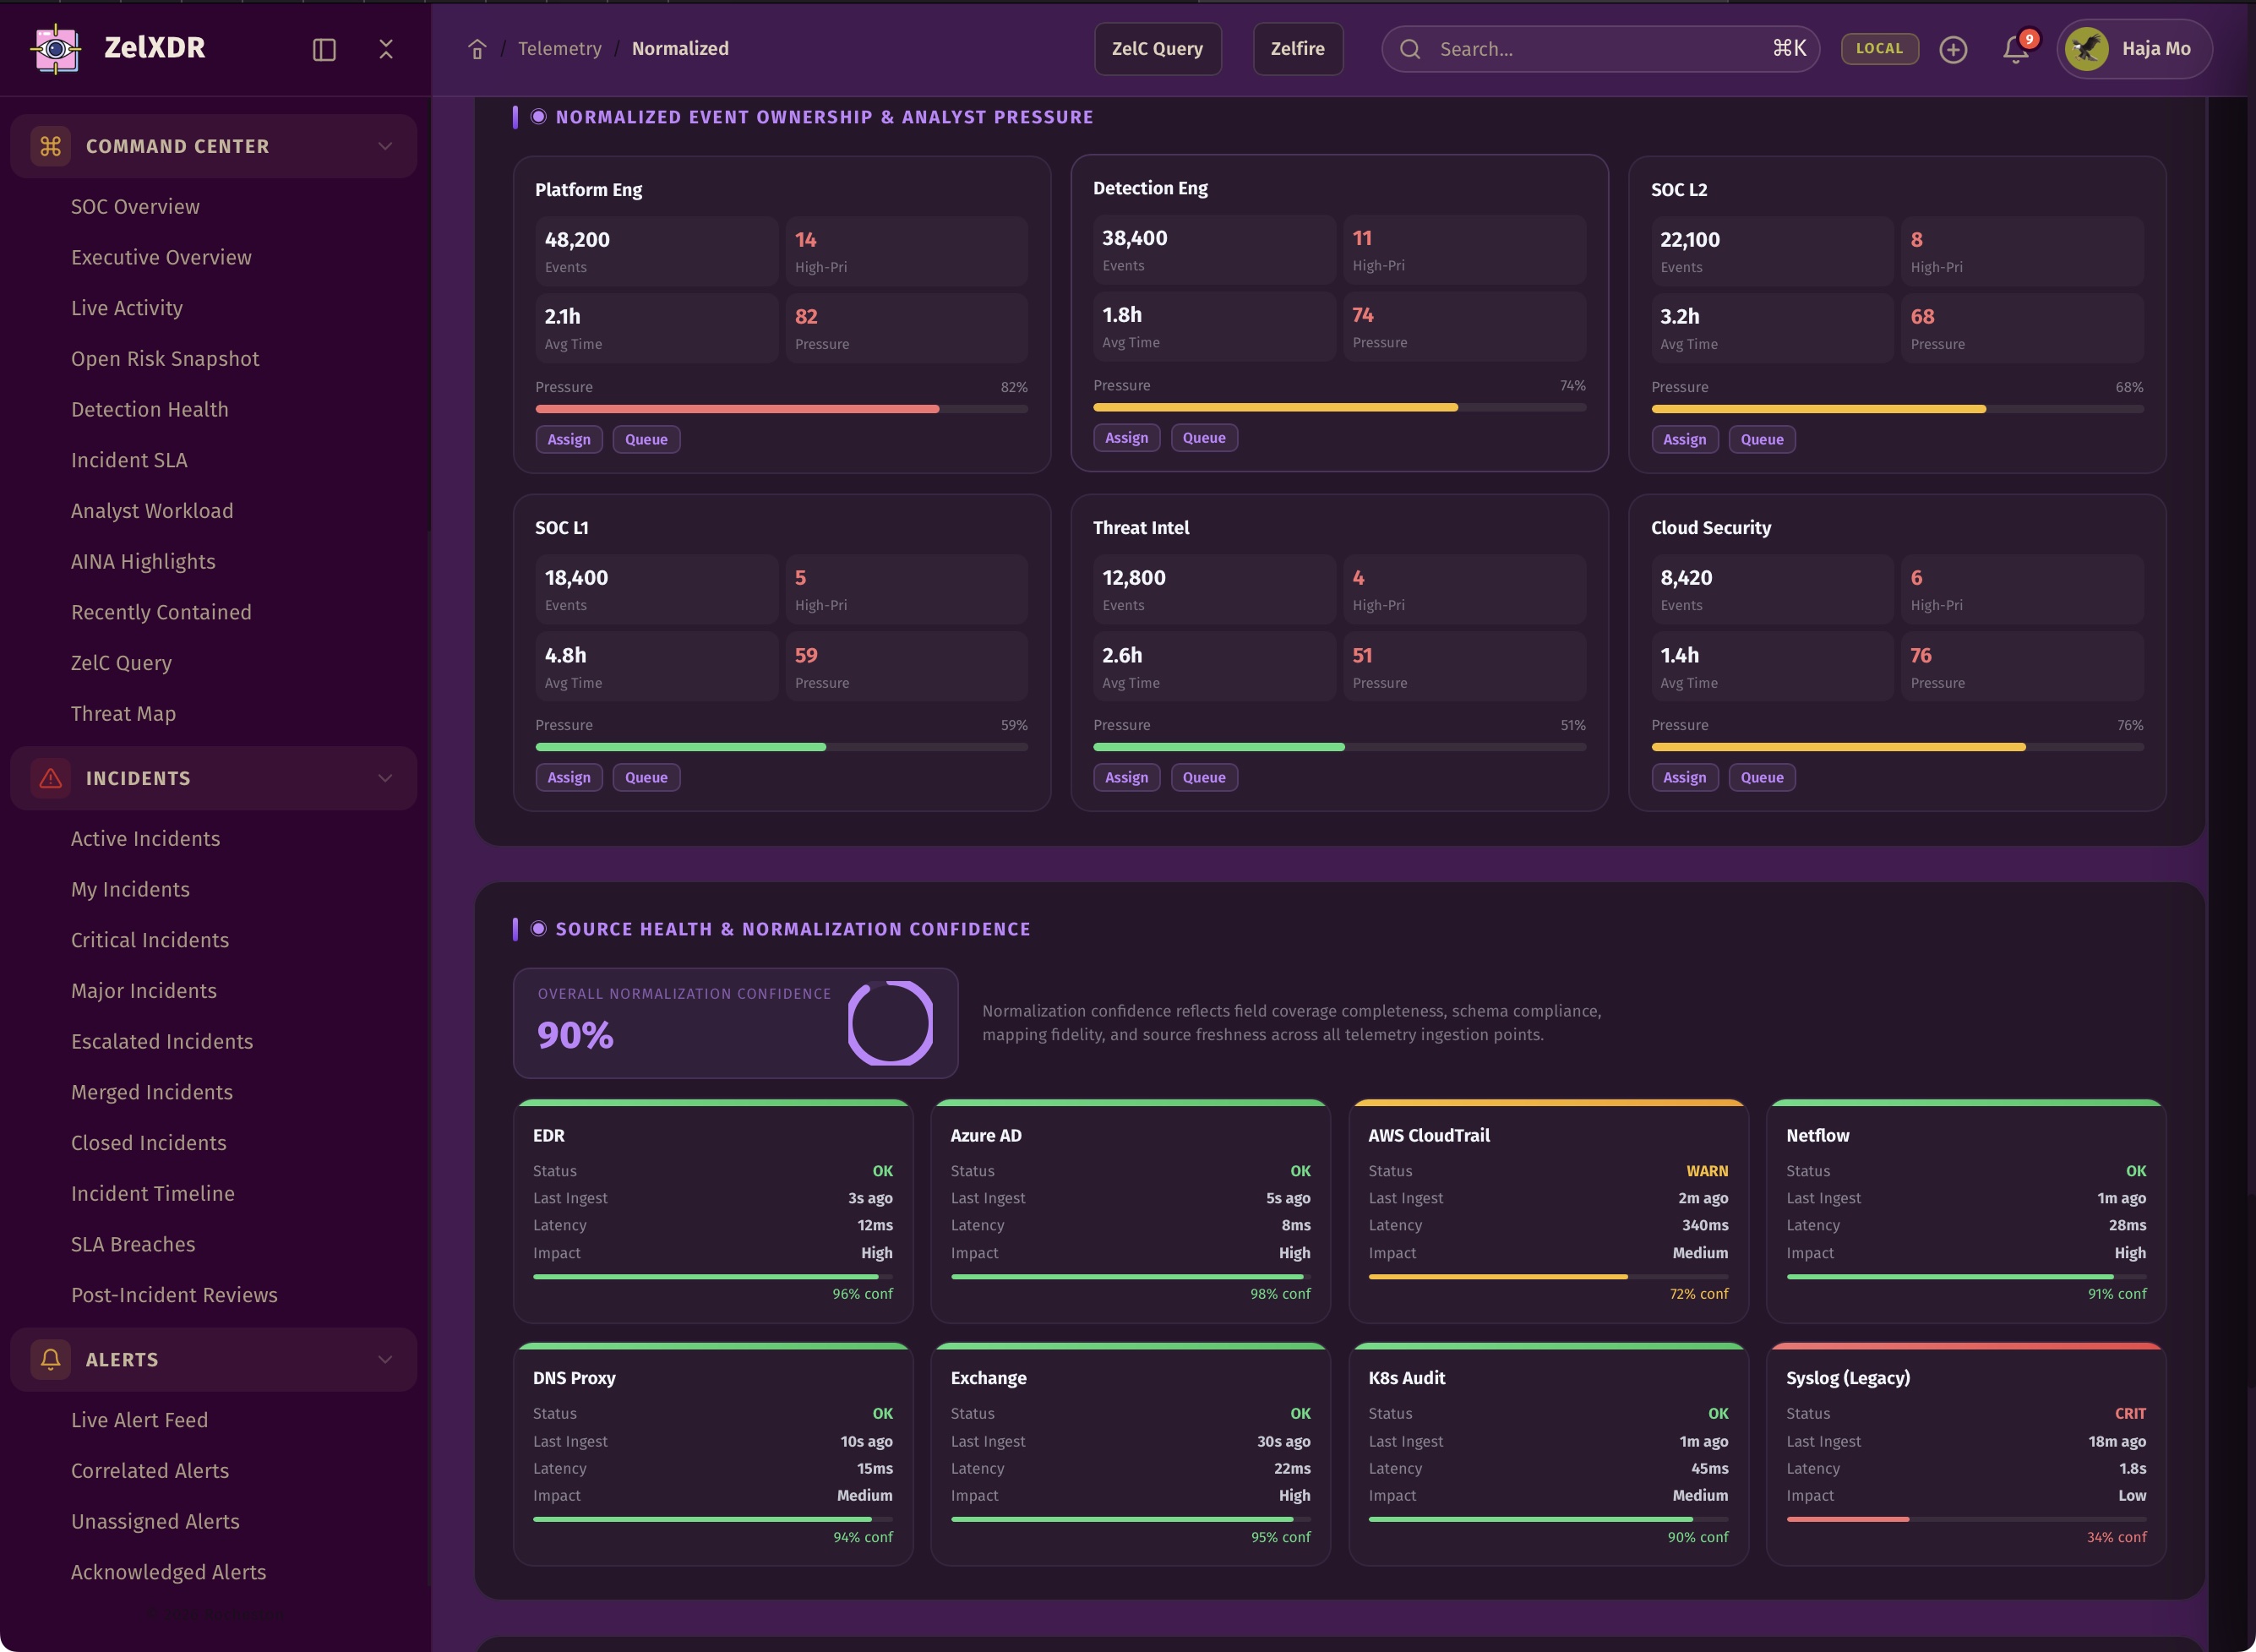
Parser Health monitors how well raw telemetry is being turned into normalized and useful events. It helps identify malformed inputs, parsing gaps, field loss, mapping issues, and other telemetry pipeline problems.
Collector Health shows the operational state of telemetry collection pipelines and source ingestion mechanisms. It helps identify delays, failures, stale streams, retry issues, and source-specific delivery problems.
Ingestion Pipelines represent the flow of data from sources into the platform. ZelXDR treats them as operational objects that can be monitored, validated, replayed, and improved to maintain confidence in the platform’s telemetry layer.
Data Latency shows how delayed different forms of security data are between source creation, ingestion, normalization, enrichment, and operational use. It is important for trust, triage, and real-time response quality.
Retention Status shows what telemetry, evidence, or operational records are still available and how retention policies affect investigations, reporting, and compliance. It supports long-term governance and forensic continuity.
ZelXDR provides asset inventory, critical asset visibility, high-risk assets, unmanaged assets, asset relationships, ownership and tag models, groupings, and exposure views. It helps analysts understand not just the threat, but what business objects that threat actually touches.
ZelXDR provides endpoint visibility through agent health, endpoint timelines, file integrity awareness, vulnerability views, isolation actions, response history, and version compliance. It helps defenders understand and control device-level risk.
ZelXDR supports user risk, sign-in analysis, impossible travel, privileged account visibility, MFA coverage, account lockouts, suspicious sessions, lateral movement signals, entitlement changes, service account behavior, and identity timelines.
ZelXDR supports cloud account visibility, subscriptions and projects, workloads, cloud activity, cloud detections, resource exposure, storage exposure, IAM changes, cloud timelines, cloud response actions, and posture summaries.
ZelXDR supports network alerts, connections, DNS activity, east-west traffic, firewall events, IDS and NDR signals, VPN activity, blocked traffic, beaconing detection, timelines, and network visibility layers.
ZelXDR supports phishing incidents, malicious attachments, malicious links, user-reported emails, quarantined messages, sender intelligence, mailbox abuse, executive impersonation, and email timelines.
ZelXDR supports IOC feeds, watchlists, indicators, malware families, threat actors, campaigns, TTP libraries, intelligence sources, feed health, enrichment history, and custom intelligence. It is meant to connect external intelligence with internal operational reality.
ZelXDR supports playbooks, active response, approval queues, containment actions, host isolation, user disable actions, IP and domain blocking, ticketing actions, automation logs, rollback history, and response templates.
Yes. Reporting is a major part of ZelXDR. The platform is intended to support executive reports, SOC reports, incident reports, hunt reports, response reports, compliance reports, operational summaries, and branded output for different audiences.
Yes. ZelXDR includes report branding concepts such as logo, title, subtitle, cover layout, classification label, footer, watermark, and report profile support so output can look premium, executive-ready, and customer-safe.
Report Templates are reusable branded report structures that can be used for executive summaries, incident reports, hunt results, compliance outputs, customer-facing reports, and other structured deliverables. They help the platform turn security content into repeatable communication.
Yes. AINA is positioned to assist with executive summaries, incident briefs, case summaries, analyst notes, and reporting language throughout ZelXDR. This allows the platform to help both operational and leadership audiences.
Ask AINA is the conversational AI interface inside the platform. It is meant to answer operational questions, explain security findings, help generate summaries, support analysts with next steps, and provide preconfigured security question prompts.
Yes. The platform direction includes an Ask AINA chatbot experience with preconfigured operational question groups such as incident analysis, alert triage, hunting, IOC analysis, blast radius, root cause, executive briefing, and false positive review.
Yes. AINA is intended to provide confidence, uncertainty, evidence-backed reasoning, suggested next steps, and structured explanation output rather than opaque answers. Explainability is treated as a core part of AI usefulness inside the platform.
Yes. The platform direction includes AINA configuration through a settings page where OpenAI API key and model configuration are stored securely and used server-side. The design expectation is that AI features should use real configured settings, not fake placeholder AI.
Yes. Integrations are one of the major platform domains. ZelXDR is intended to connect with APIs, webhooks, SIEMs, cloud platforms, endpoint tools, identity systems, ticketing systems, threat intel feeds, and custom enterprise connectors.
The integration model is broad and includes API integrations, webhook integrations, cloud integrations, SIEM integrations, endpoint integrations, identity integrations, ticketing integrations, threat intelligence feeds, and custom enterprise source connectors. The goal is broad platform connectivity rather than narrow point features.
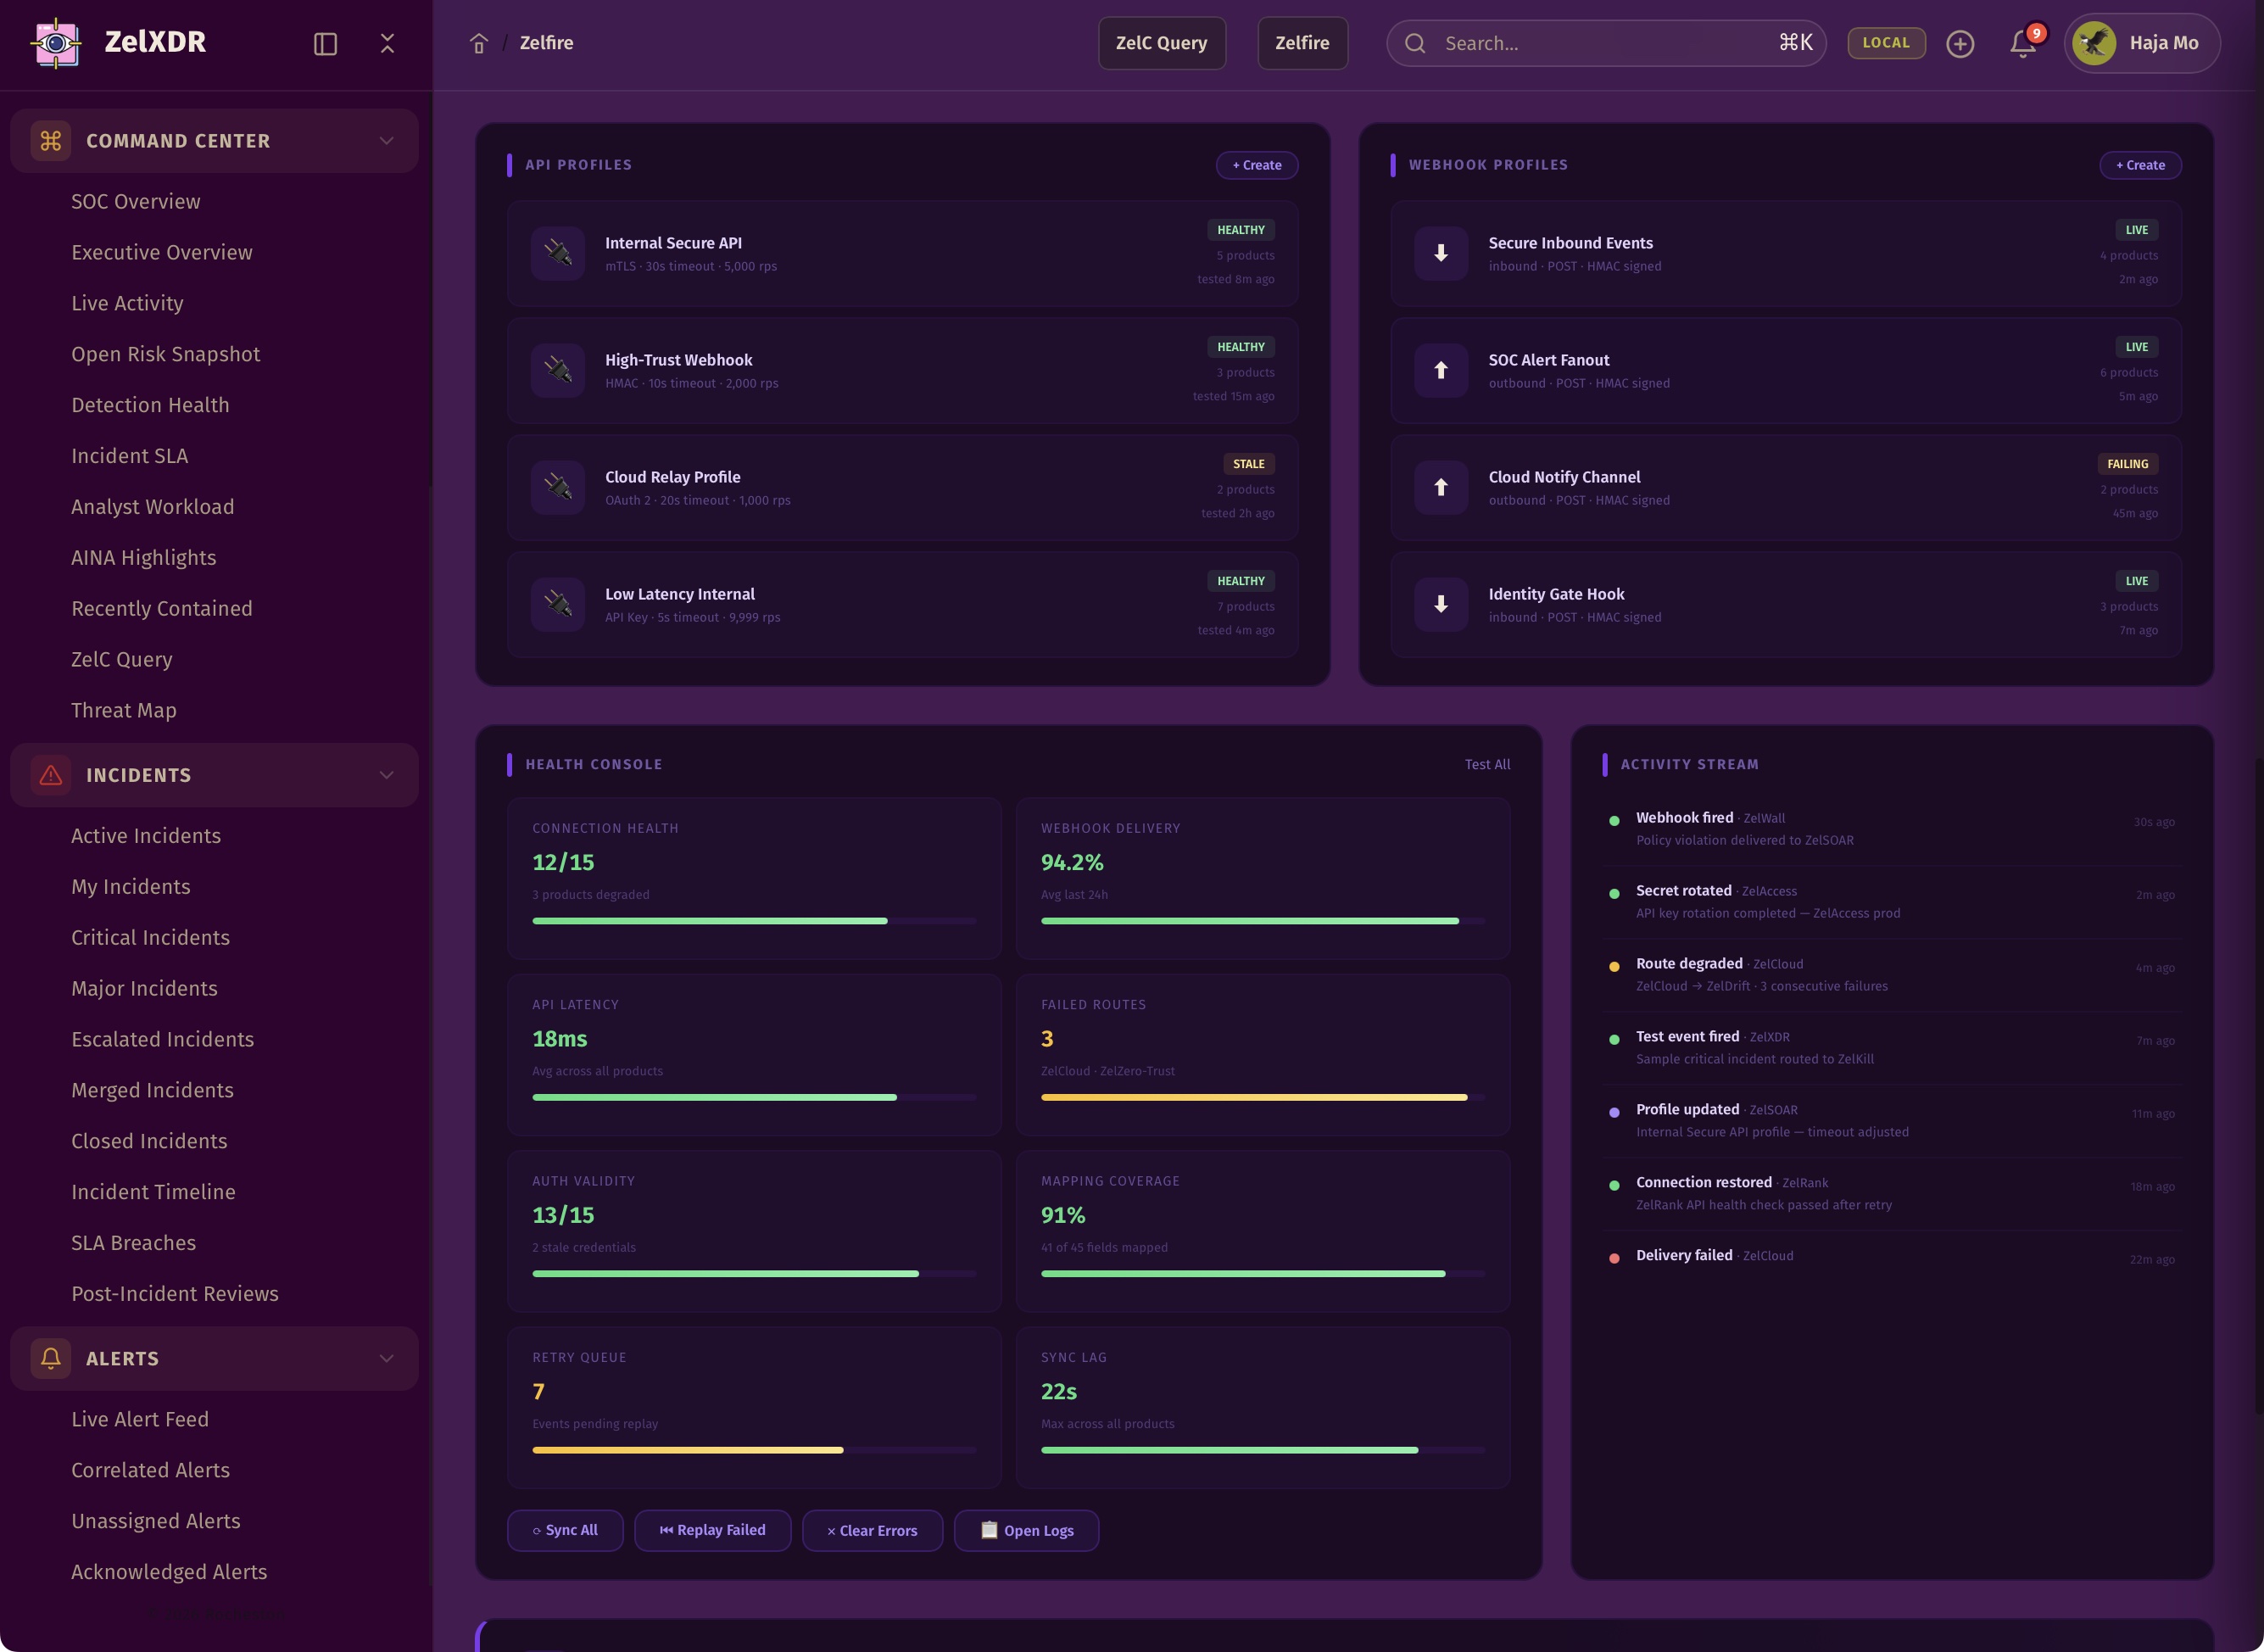
Yes. Webhooks and APIs are first-class integration patterns in ZelXDR. They are intended to support inbound and outbound workflows, connection tests, routing, authentication, mapping, replay, rotation, and logging.
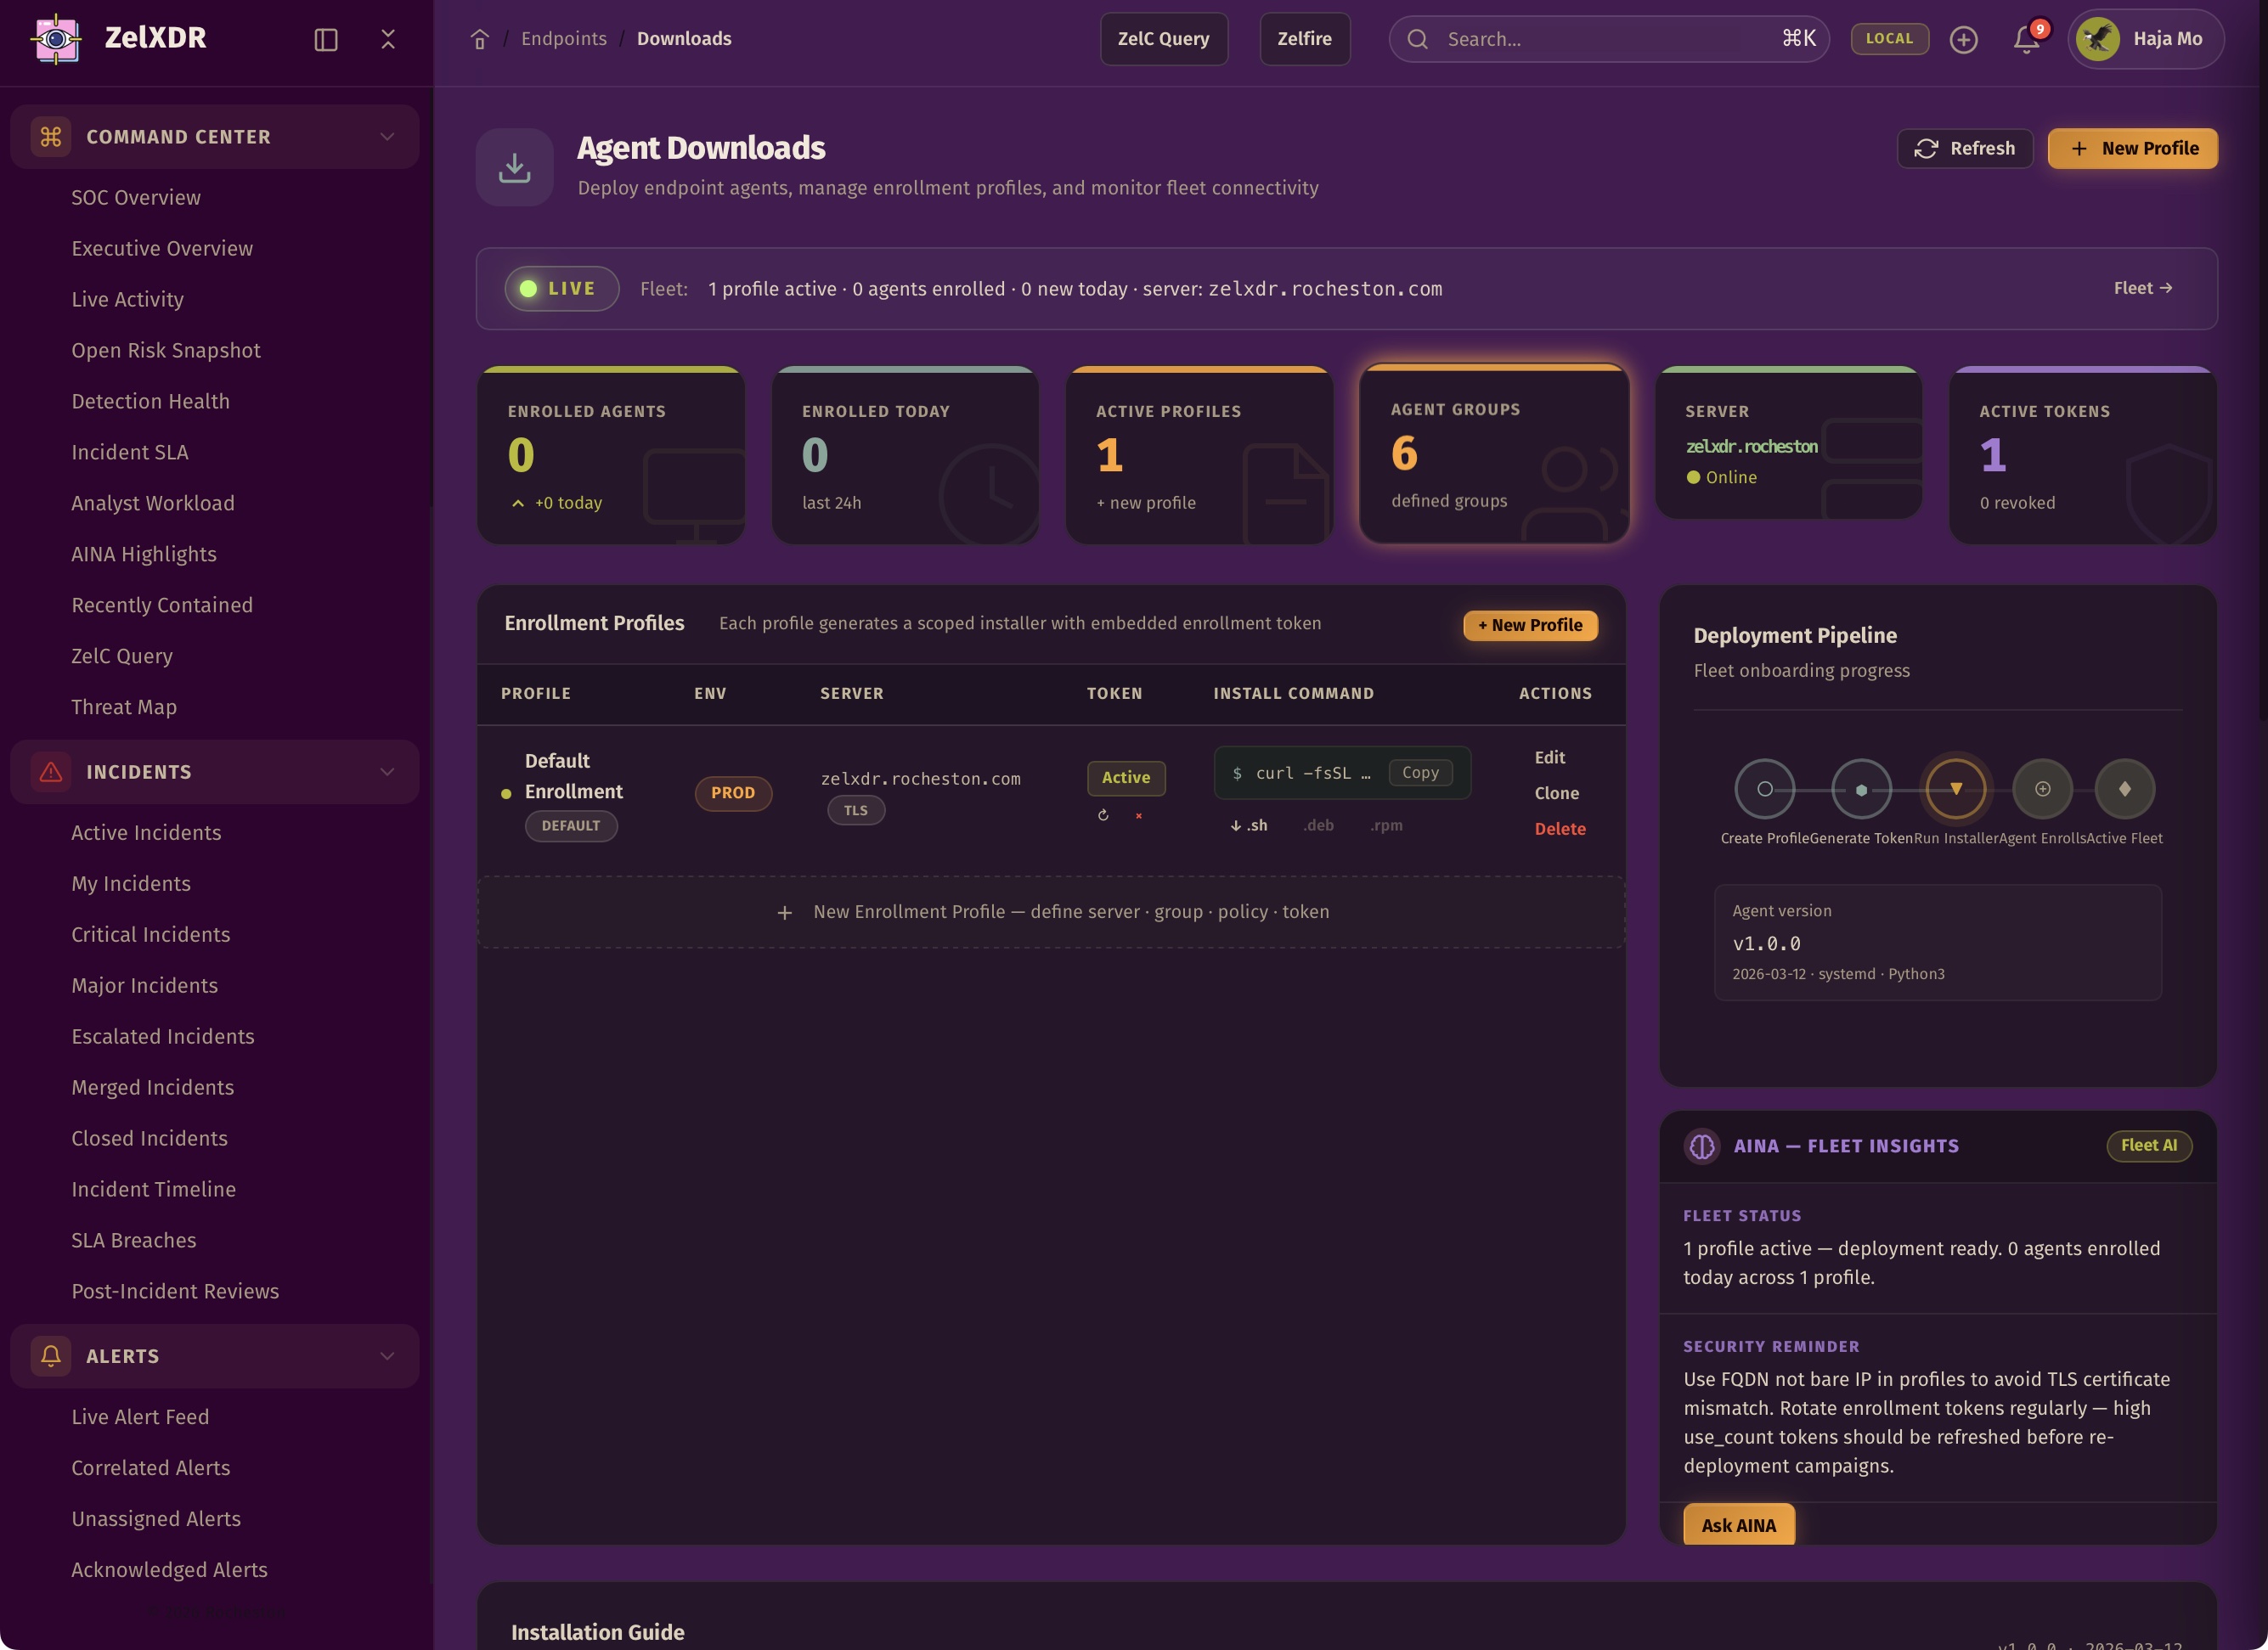
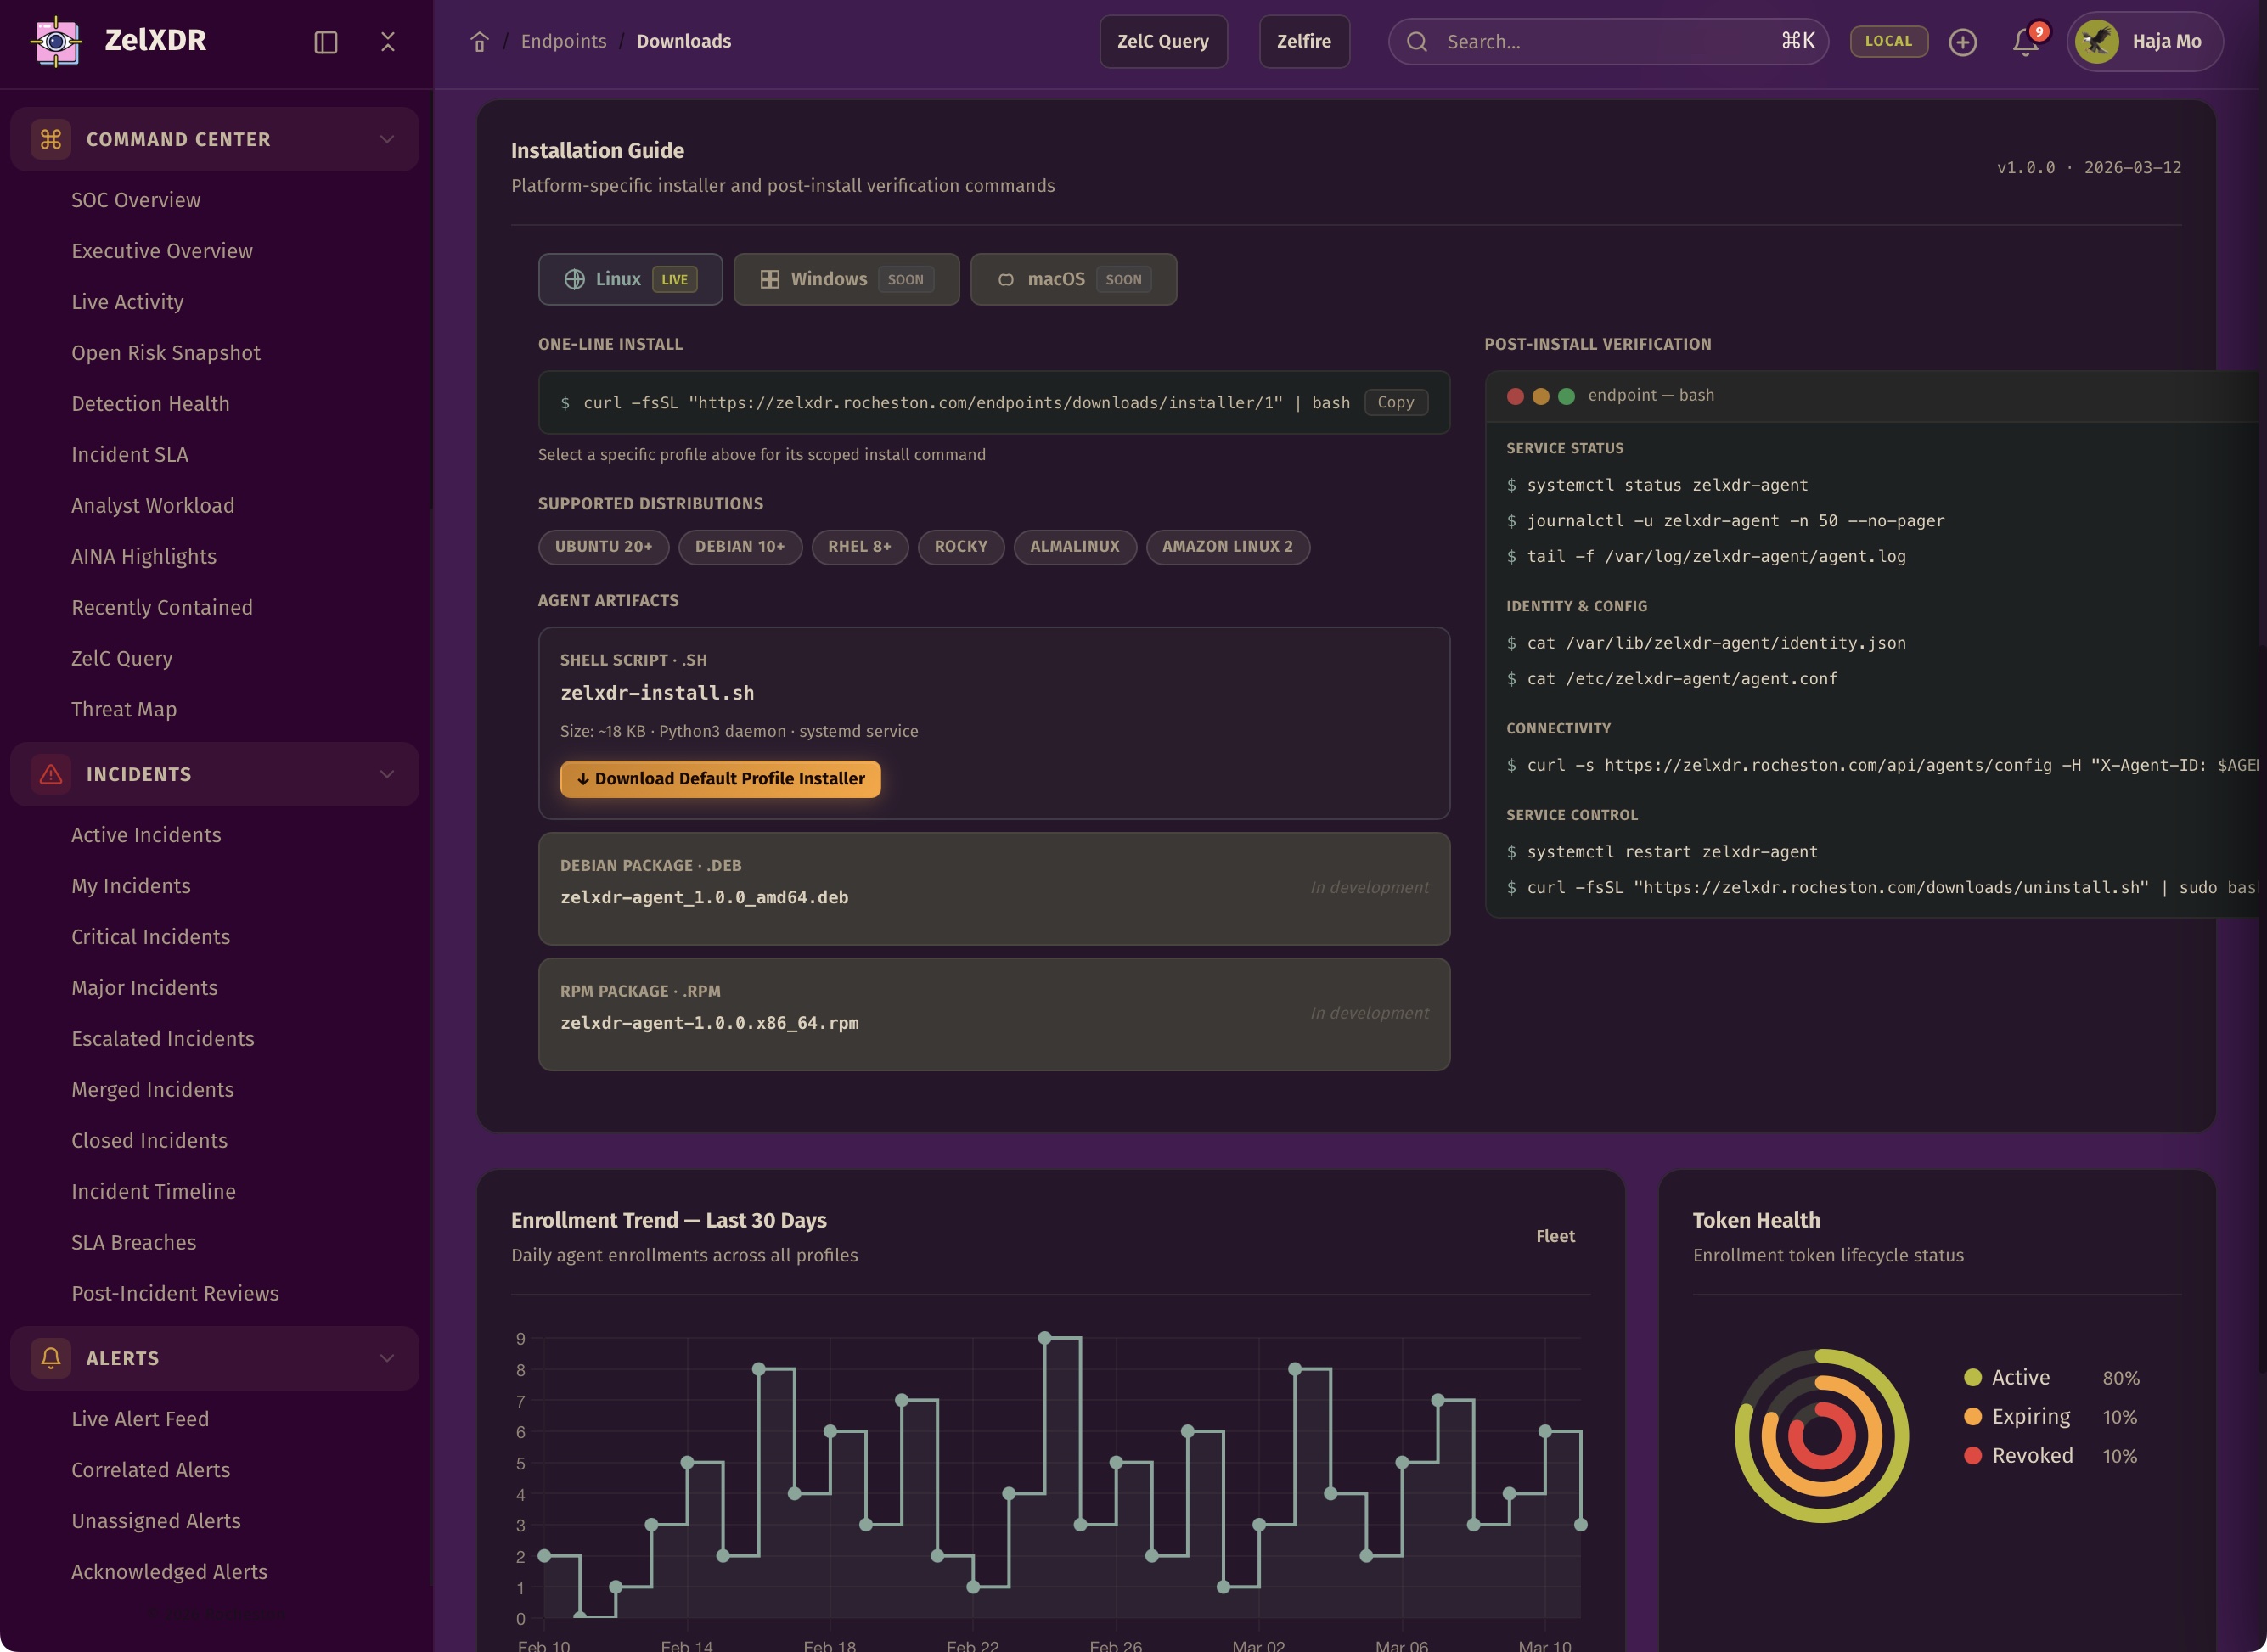
Yes. The platform includes agent management and agent download concepts, including Linux-focused deployment, server connection, grouping, naming, heartbeats, and integration into the larger endpoint visibility workflow.
Yes. The intended agent enrollment model supports connection to the platform using configured domain or IP settings. It is designed to allow real enrollment flows, grouping, custom names, and visibility inside endpoint management experiences.
Yes. Linux is explicitly emphasized in the endpoint agent model and deployment workflow. The goal is not merely cosmetic support, but a real operational agent lifecycle for Linux systems.
Threat Graph is a Command Center experience that visualizes live or simulated threat flows over a world map using animated routes, pulses, heat zones, and campaign-like motion. It is intended as a premium SOC display and visual command surface.
Zelfire is positioned as a premium internal product-fabric page for the Zelfire family of products. It is intended to show product tiles, product-to-product routes, API configuration, webhook configuration, and operational connection patterns between ecosystem components.
ZelC Query is a full editor-and-terminal style page where users can write ZelC code in a Monaco-like editor, run simulated security commands, load sample files, use templates, and view realistic terminal output tied to the Zelfire ecosystem.
Yes. The intended experience supports sample file loading, template insertion, script saving, command execution simulation, and varied terminal responses so the page feels like a real operational security language console.
Yes. Administration includes users, roles and RBAC, teams, groups, approvals, notifications, labels, secrets, certificates, retention, backup and restore, and audit logs. Governance is treated as part of platform trust, not a secondary feature.
ZelXDR includes user management, RBAC, teams, groups, approvals, notifications, secrets management, certificate tracking, data retention, backup and restore, audit logs, AI settings, branding settings, and sidebar or UI preferences. The platform is designed to govern itself as carefully as it governs threats.
Yes. Secrets Management and Certificates are explicit administrative domains. The platform is designed to track status, expiration, rotation pressure, linked dependencies, and related governance risk.
Yes. Backup and Restore is a first-class administrative capability. It is intended to show backup health, restore readiness, recovery confidence, and administrative governance around platform continuity.
Yes. Audit logging is part of the administration model. The expectation is that important administrative actions, configuration changes, approvals, AI actions, and governance-sensitive changes are tracked and reviewable.
ZelXDR can support executive security summaries, board risk summaries, SOC operational reports, incident reports, hunt reports, AI incident briefs, AI triage summaries, vulnerability exposure reports, endpoint health reports, telemetry quality reports, compliance assessment outputs, and many more structured security reports.
Yes. The reporting and template model explicitly includes customer-safe and internal-only modes. This allows the same platform to serve operational, executive, and external communication needs with branding and classification awareness.
Yes. Executive briefing generation is a core AI and reporting use case in ZelXDR. AINA can help write executive summaries, incident briefings, business impact summaries, and board-ready language from operational data.
Yes. False positive review is embedded into AI triage, AI incident understanding, rule tuning, QA, alert analysis, and hunt result review. The platform is designed to reduce noise rather than just display it.
Yes. ZelXDR includes dedicated MITRE mappings and is meant to connect rules, hunts, results, and findings to tactics, techniques, and sub-techniques. MITRE context is treated as operational coverage, not just documentation.
Yes. ZelXDR is designed to help translate technical security activity into executive-readable summaries, business impact language, stakeholder updates, and high-level reporting through both native reporting and AINA-driven writing.
Yes. The reporting and template architecture is intended to support executive audiences, internal operations, compliance audiences, and customer-safe reporting. This includes both technical and business-style communication outputs.
Yes. Detection Change Log, approvals, QA, version history, and governance-related workflows are all part of the platform direction. Change is meant to be observable, reviewable, and tied to operational trust.
Yes. Reusable knowledge is supported through hunt templates, saved hunts, report templates, report branding, knowledge center content, lessons learned, notes, playbooks, and AI-generated summaries. The platform is designed to retain and scale organizational knowledge.
ZelXDR is built around the idea that security operations should feel unified, explainable, and operationally usable. Instead of forcing teams to manage fragmented tools and isolated data, it tries to create a platform where signals, reasoning, workflows, reporting, and action all work together.
ZelXDR is positioned as a daily operational platform. Its modules, workflows, AI features, endpoint capabilities, reporting, hunts, telemetry exploration, and administrative functions are all described as ongoing daily-use surfaces, not occasional showcase pages.
Yes. ZelXDR is intended to cover the full lifecycle from event ingestion and normalization to alert triage, AI incident understanding, hunts, anomalies, investigations, cases, endpoint response, reporting, and governance. The vision is end-to-end operational continuity.
AI through AINA acts as an operational intelligence layer rather than a decorative add-on. It is designed to support triage, summarization, explanation, investigation acceleration, reporting, executive communication, and next-step decision support across the whole platform.
ZelXDR is important because it aims to reduce the fragmentation, confusion, and delay that often define modern security operations. It provides a way to bring signals, reasoning, workflows, control, and communication into one platform so teams can work with more clarity and less waste.
ZelXDR is an AI-powered security operations command platform in the Zelfire ecosystem that unifies detection, investigation, threat hunting, endpoint control, telemetry analysis, reporting, and governance into one premium operational experience built by Haja Mo and positioned as part of the RCCE-exclusive Zelfire environment.
No matching questions. Try another word or clear the search.
Discover the rest of Rocheston Zelfire and see how AINA connects intelligence across your security workflow.
LET’S GET STARTED
Talk to Rocheston about your environment, product access, and the workflows your team needs.
Request access