Continuous verification
Evaluate access using identity, device, and workload context.
ZERO TRUST ARCHITECTURE
Verify every access decision.
ZelZero-Trust combines least privilege, micro-segmentation, and continuous verification. AINA helps teams adapt access decisions using behavior, context, and risk across users, devices, and workloads.
Zero Trust architecture
BUILT FOR YOUR WORKFLOW
Evaluate access using identity, device, and workload context.
Limit access to the permissions needed for the task.
Establish boundaries that help contain threats within the environment.
THE COMPLETE PRODUCT GUIDE
Get to know the capabilities, workflows, and intelligence behind the product.
A redesigned Zero Trust experience for teams that want deep context, beautiful control surfaces, and precise access decisions across applications, identities, devices, sessions, networks, data, and AI agents.
MFA strength, trusted browser, and compliant device posture satisfy policy.
Unmanaged contractor device detected outside approved network zone.
AINA flags high blast radius for a broad access group before rollout.
Model outcomes, compare scenarios, and forecast blast radius before enforcement.
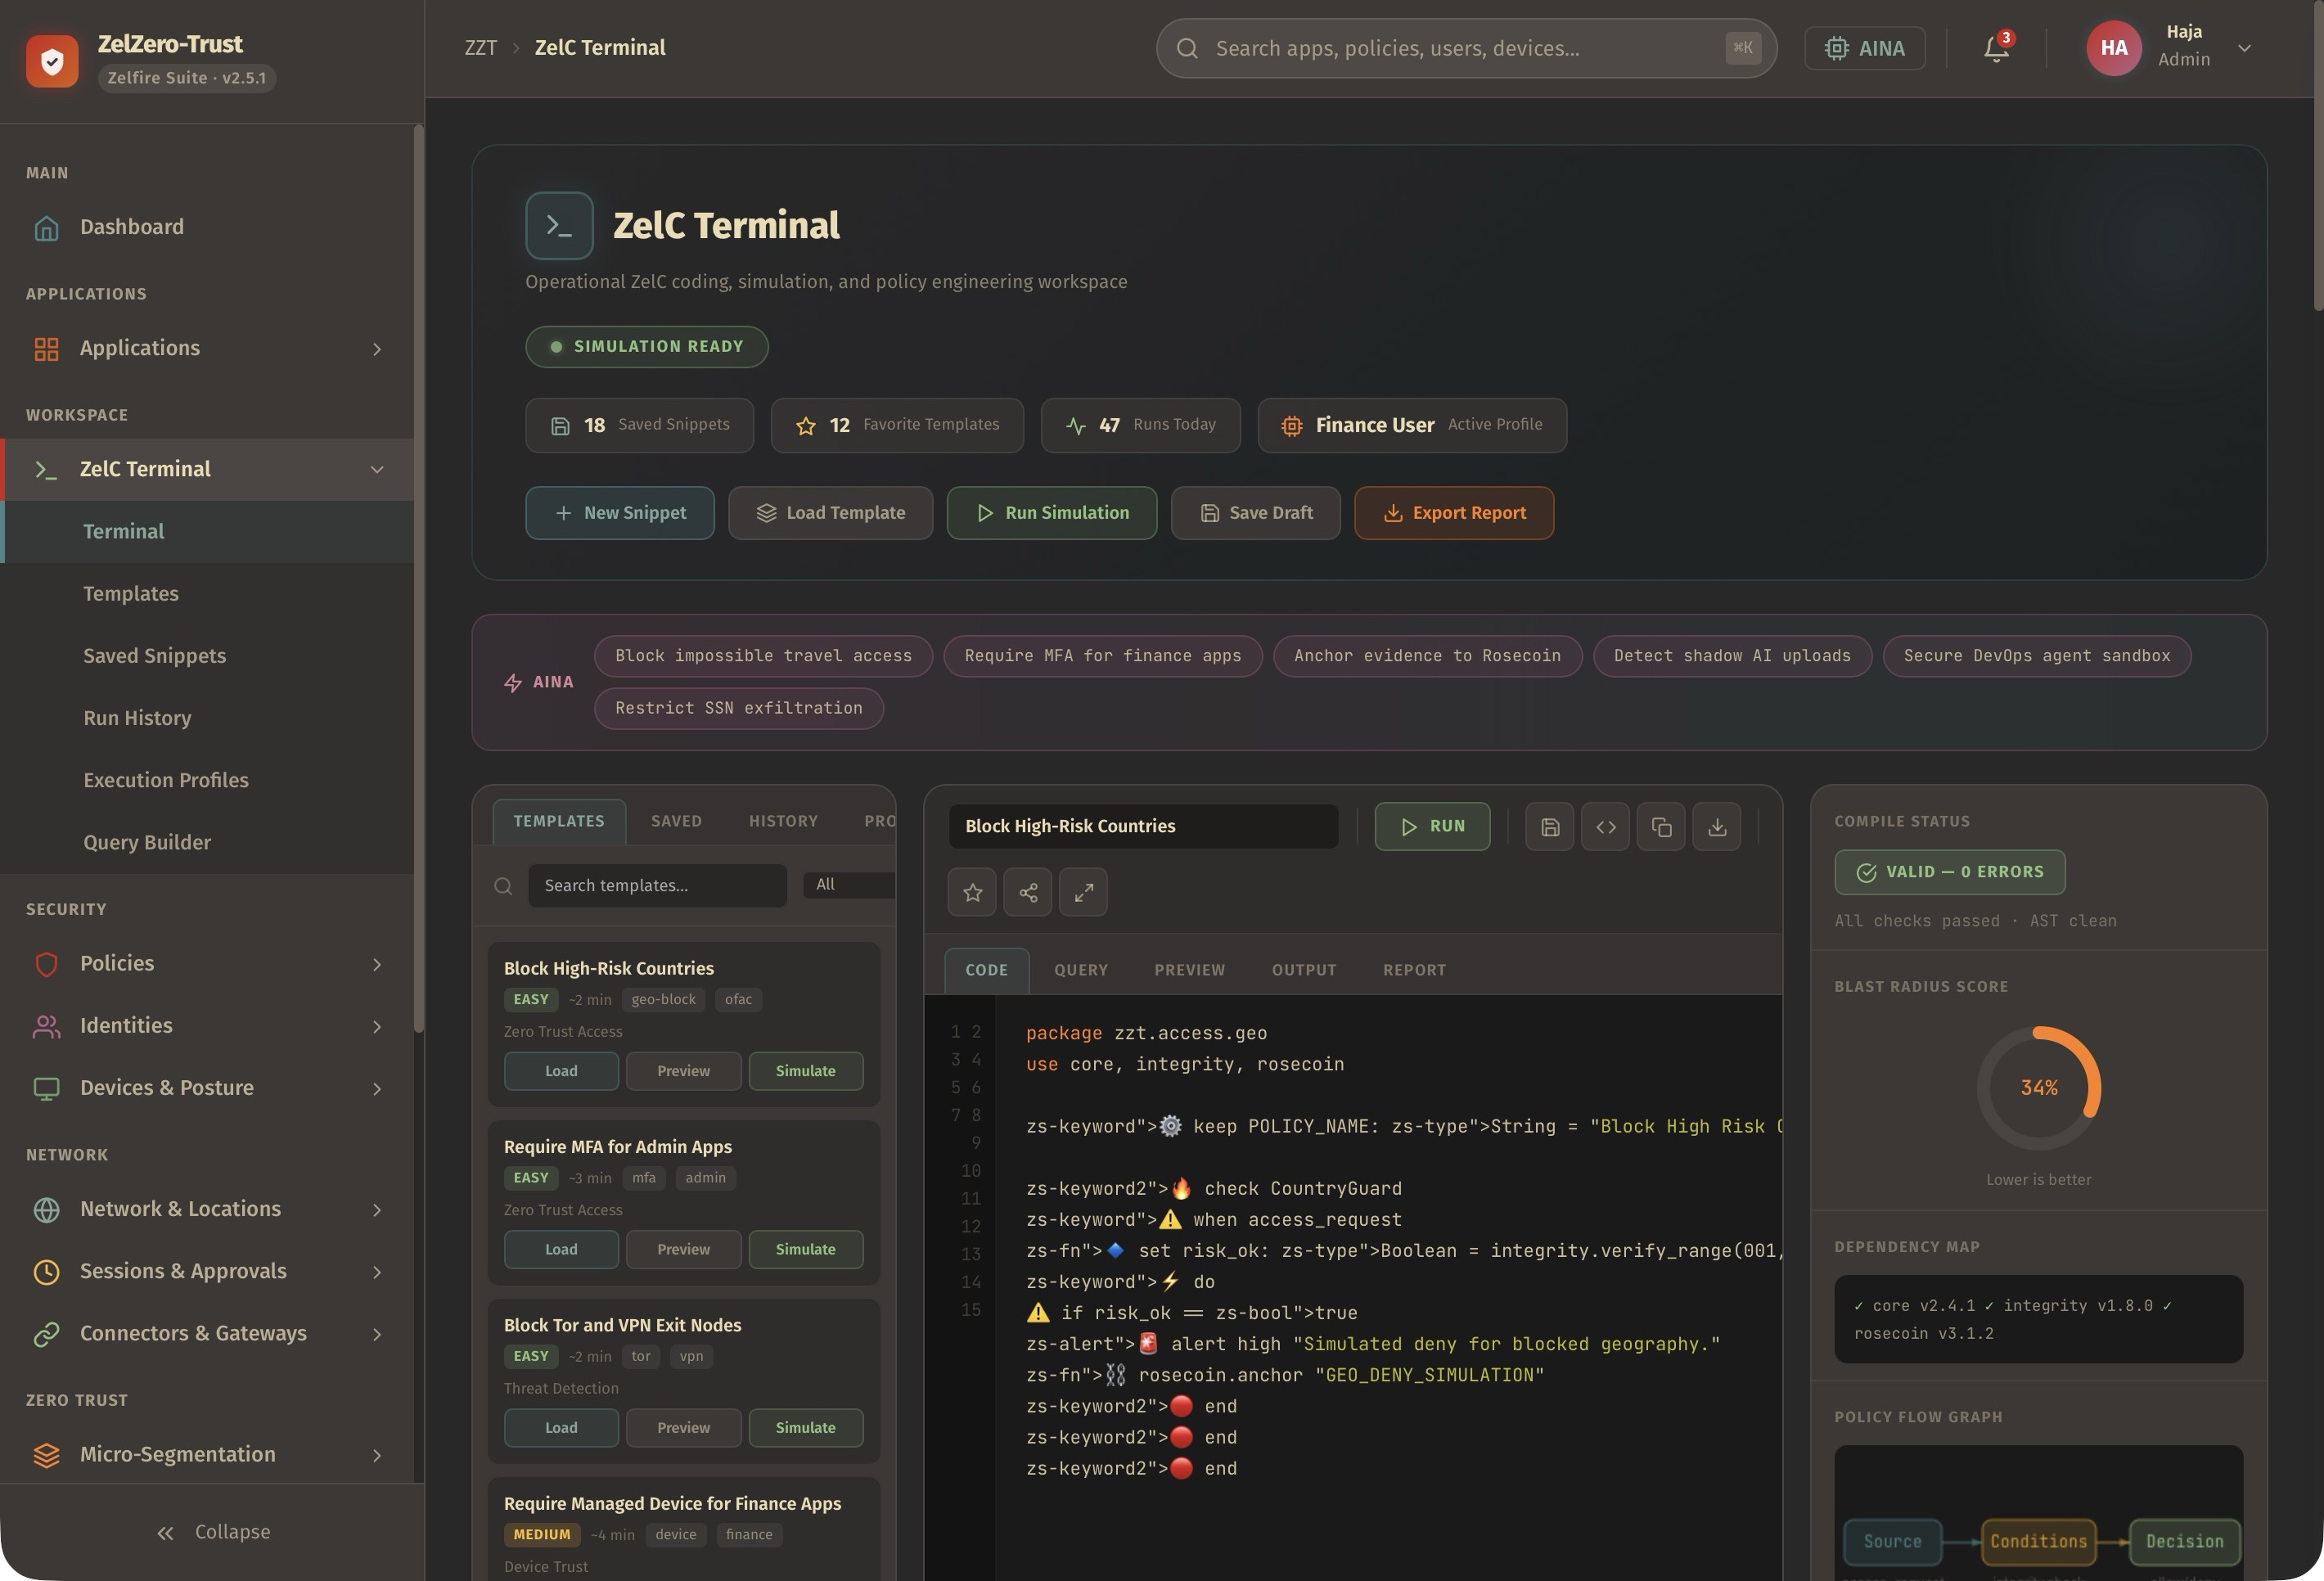
Generate, test, and trace Zero Trust logic inside a security-native workspace.
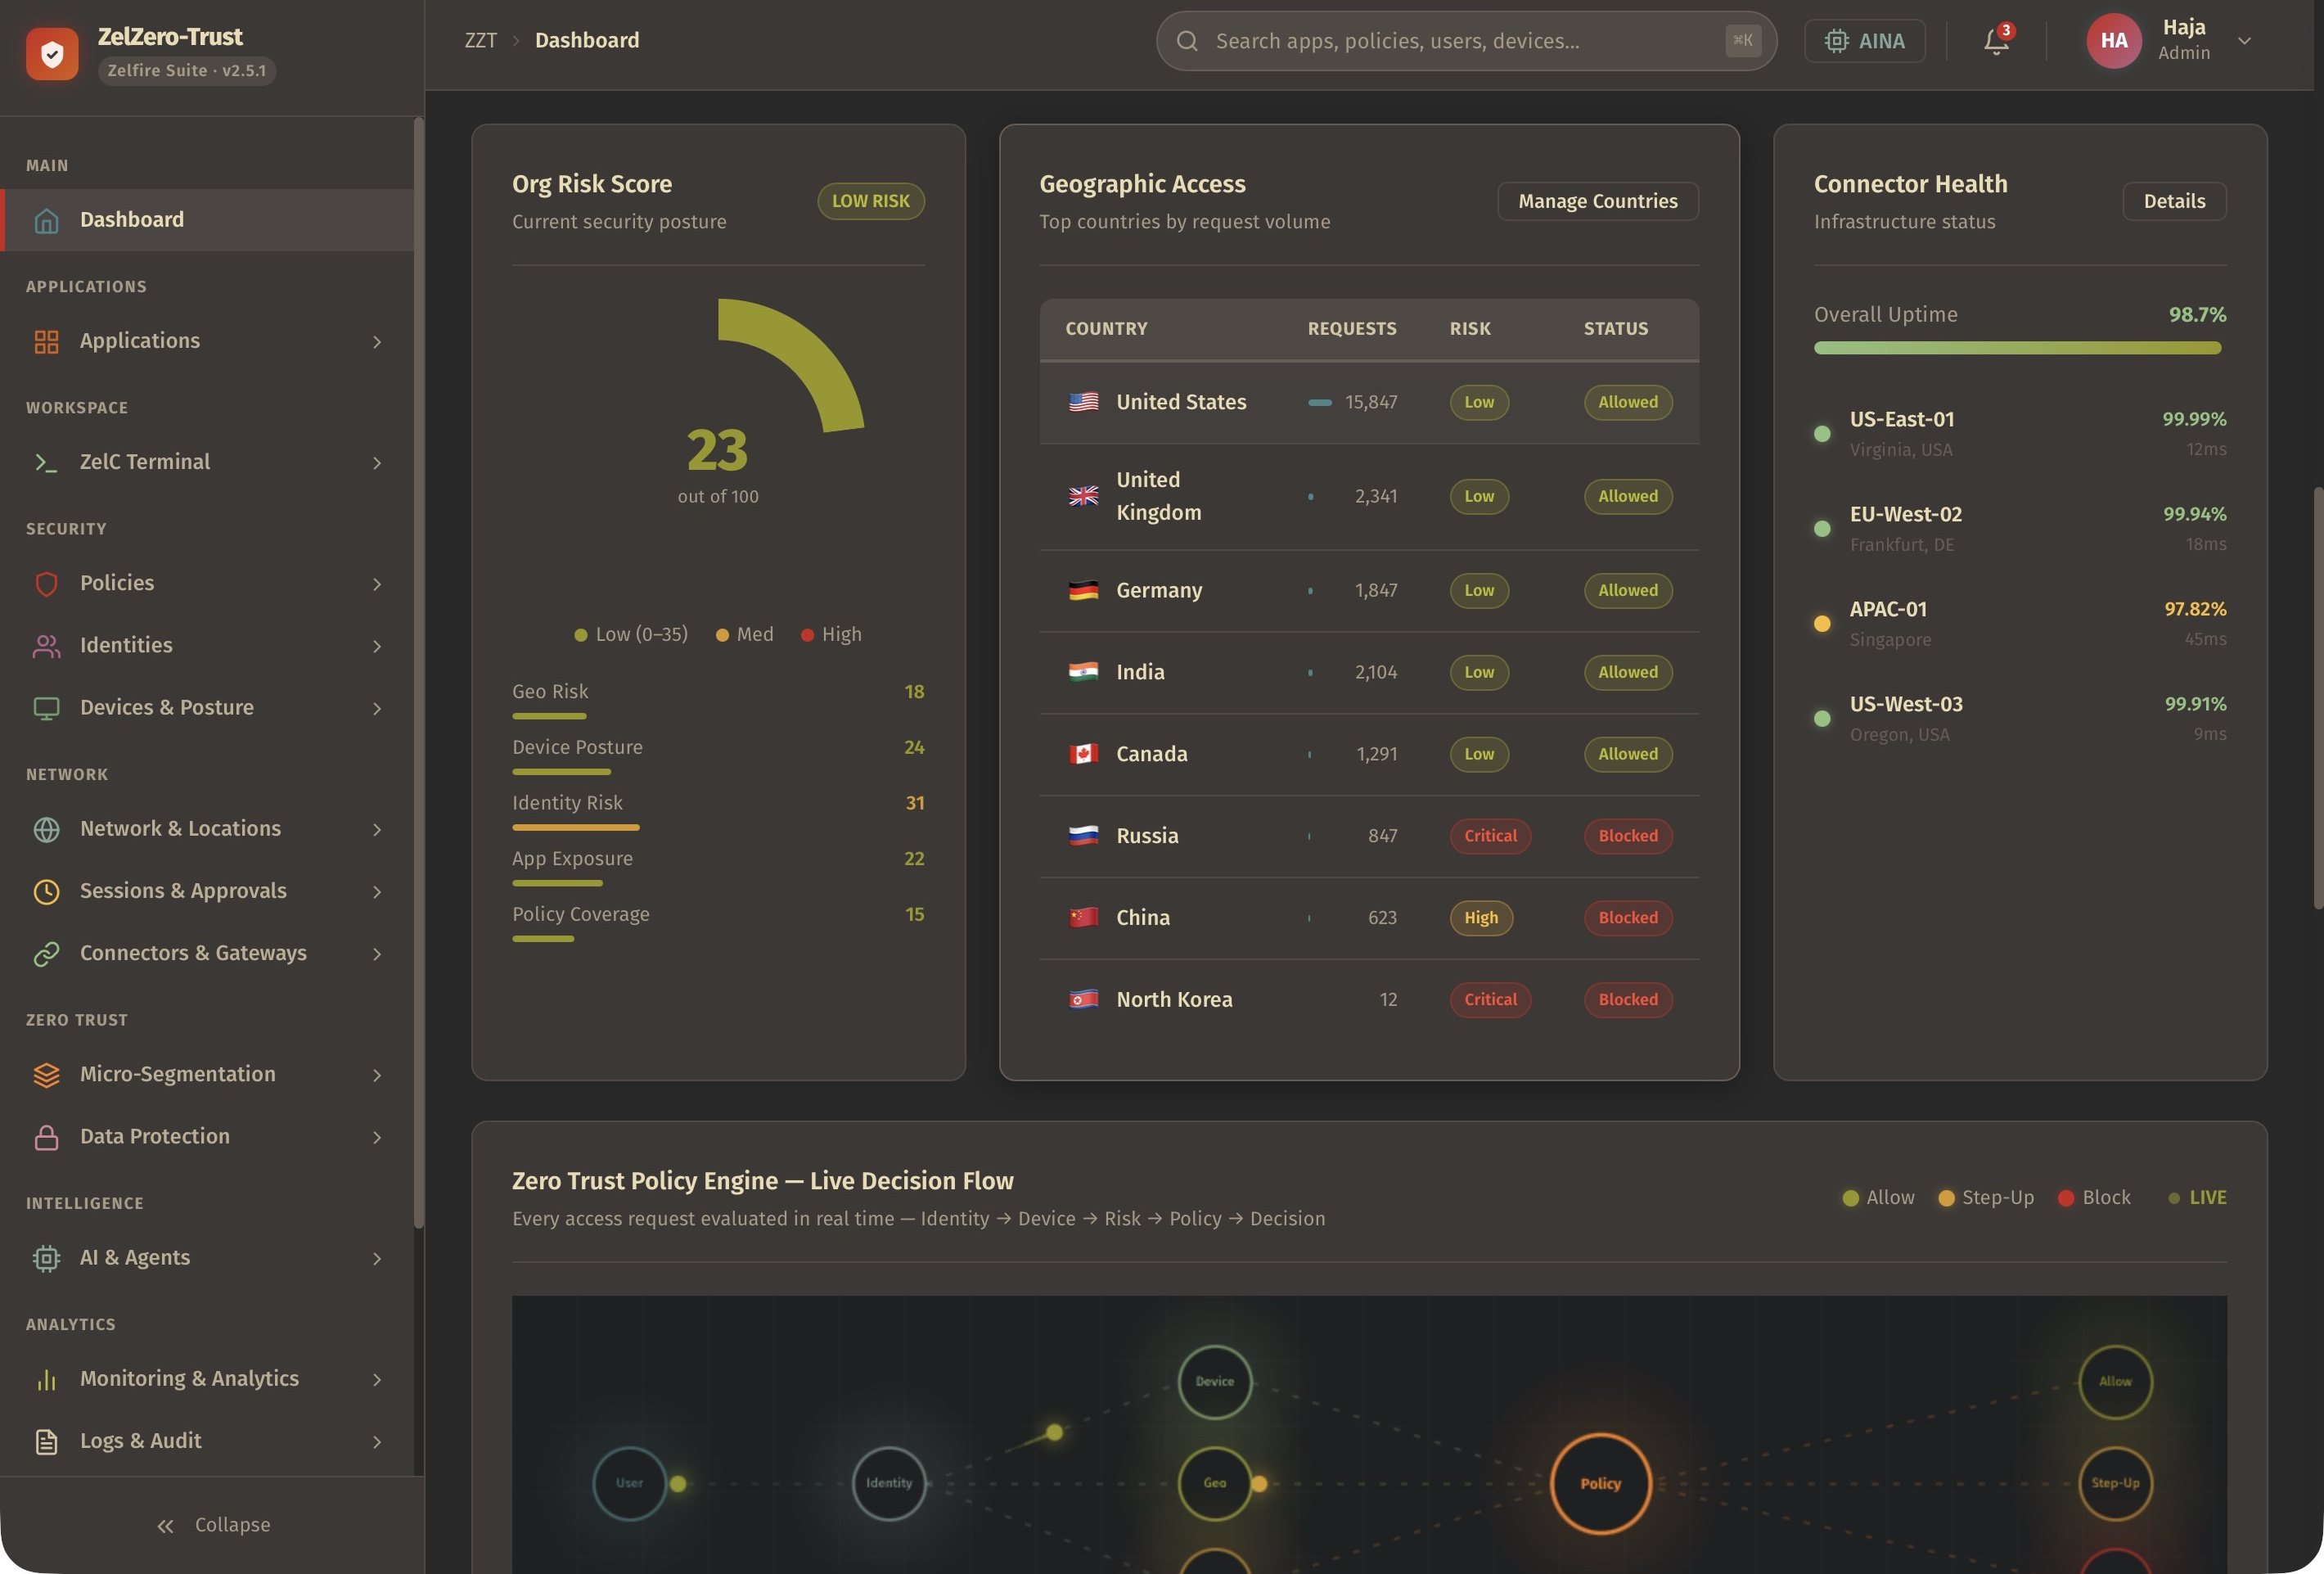
Every access decision re-evaluates who, what, where, how, and risk in the moment.
Surface reasoning, friction, remediation, and rollout guidance in plain language.
Unify access, reviews, segmentation, and data safeguards in one operating model.
Write policy logic, load templates, and inspect execution traces before activation.
ZelZero-Trust replaces network-era assumptions with a continuous, policy-driven trust fabric that can explain itself, adapt in real time, and stay beautiful while doing serious work.
Traditional security often trusts too early. VPN-style access, weak browser hygiene, stale service accounts, unmanaged contractor devices, over-broad partner access, and unreviewed exceptions all increase blast radius.
ZelZero-Trust unifies access, governance, analytics, remediation, and AI-powered explanation into one experience. Teams can protect apps, review blast radius before changes, enforce least privilege, and keep posture and trust aligned over time.
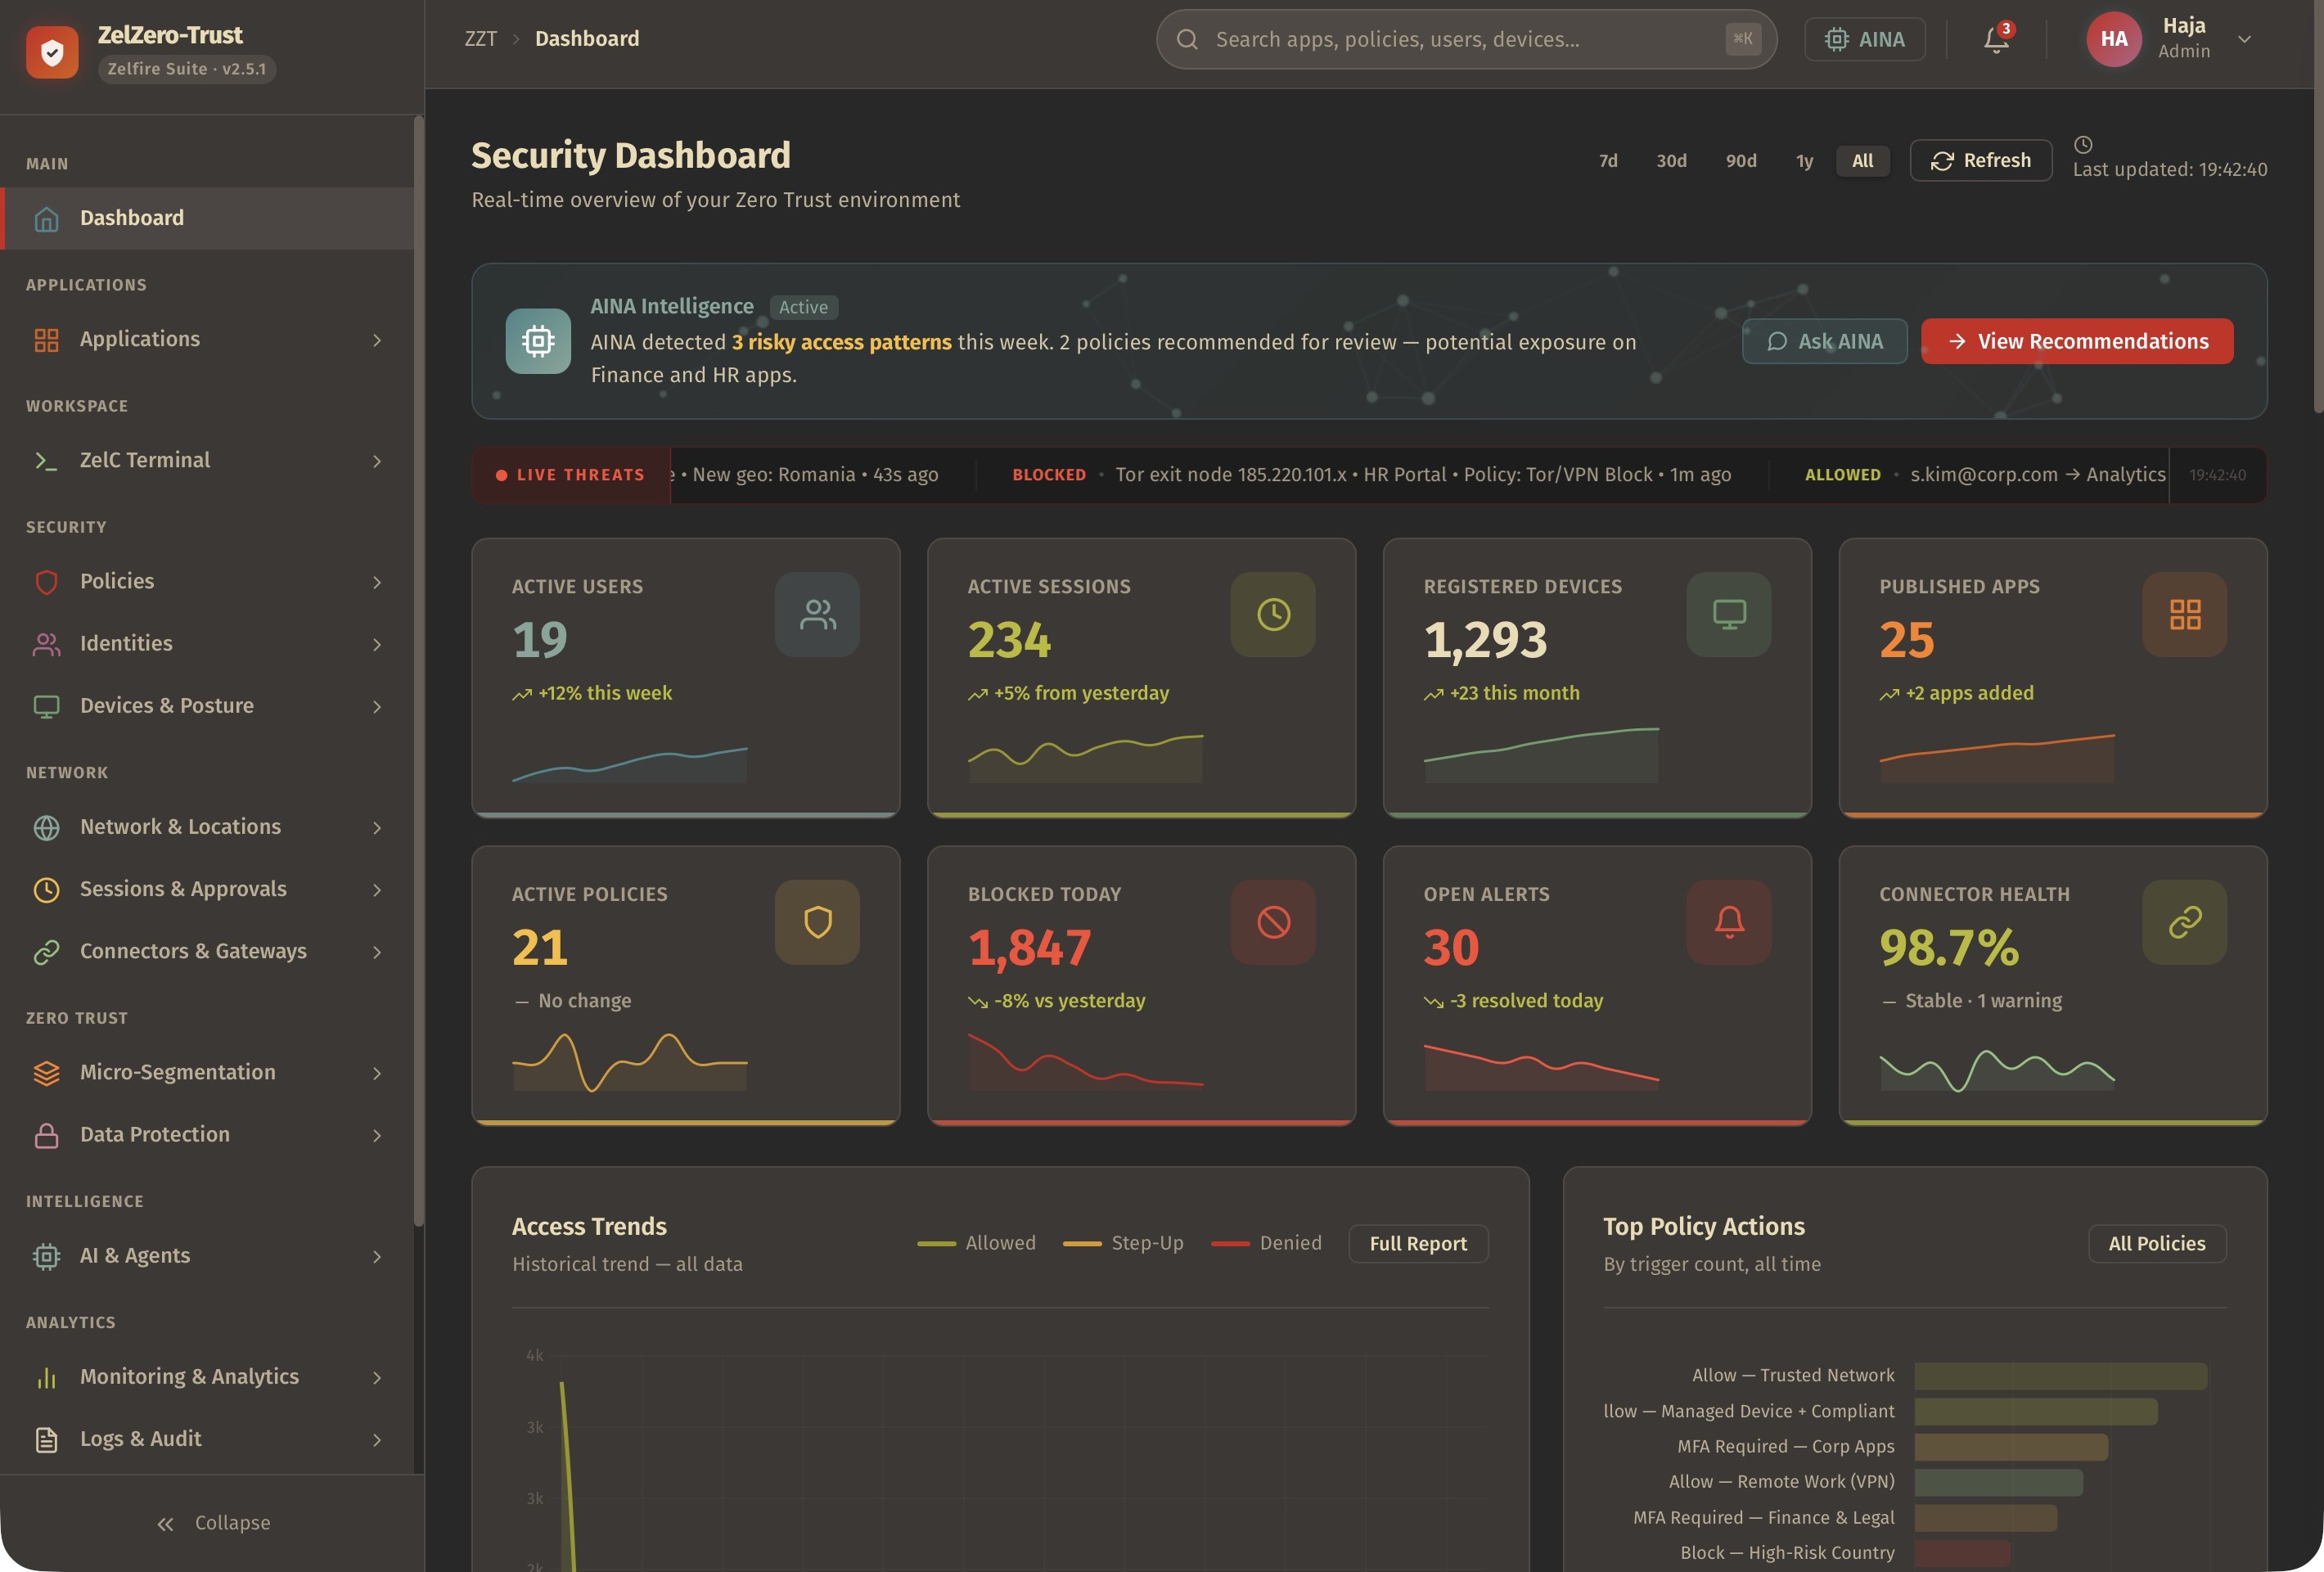
Evaluate identity, device, browser, network, location, session, and risk before and during access.
Explain decisions, suggest safer configurations, predict friction, and highlight cleanup opportunities.
Model matched policies, failed conditions, exceptions, readiness, and blast-radius estimates before rollout.
Work in a security-native coding and simulation environment with templates, generated logic, and traces.
Pull identity, posture, network, browser, and session context into one real-time decision layer.
Use simulator and report-only testing to preview friction, blast radius, and policy reach.
Let AINA translate policy behavior into plain language with remediation and cleanup guidance.
Roll out with governance, reviews, analytics, and feedback loops that keep trust current.
Evaluates identity, device, browser, network, location, session, and risk before and during access.
Protects web apps, private apps, SaaS apps, APIs, admin consoles, partner portals, and internal tools.
Manages users, groups, external users, partners, service accounts, agent identities, and access reviews.
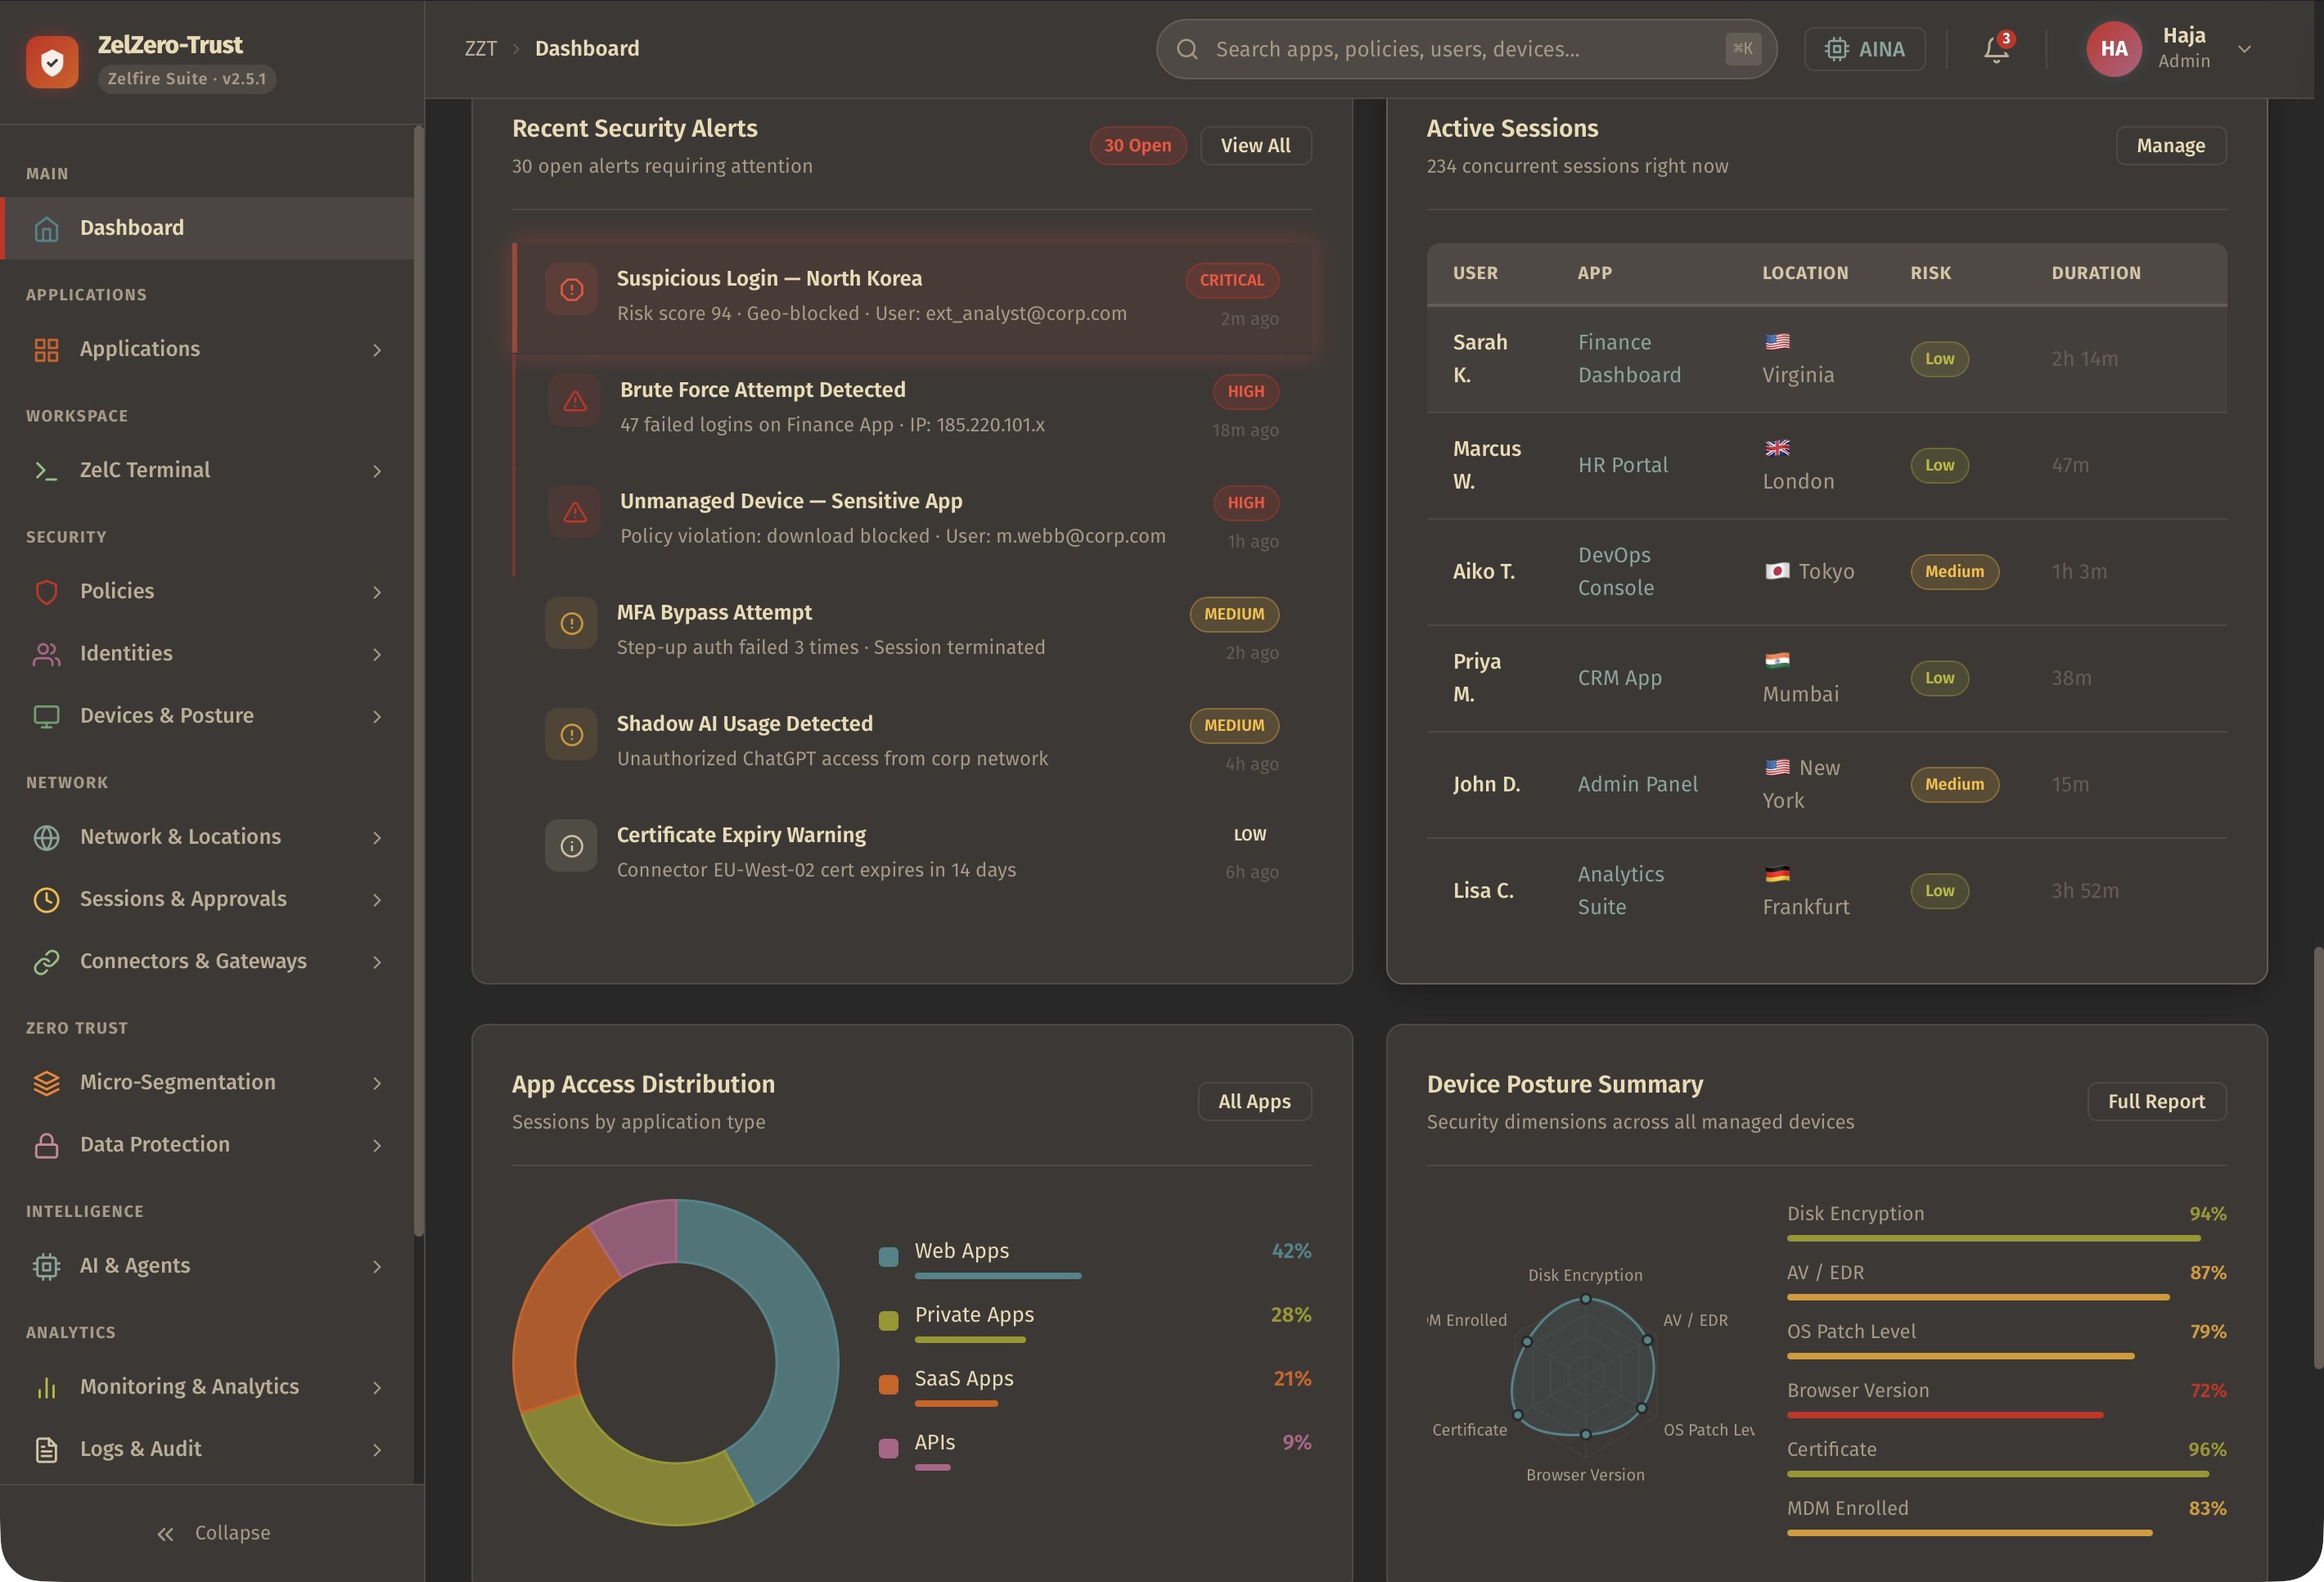
Checks encryption, EDR, MDM, OS version, patch level, firewall, secure boot, TPM, and device certificates.
Enforces browser family, minimum version, trusted extensions, enterprise browser rules, and browser-only controls.
Supports idle timeout, absolute timeout, reauthentication, session downgrade, anomaly response, and termination.
Uses countries, named locations, GPS zones, IP ranges, ASNs, ISPs, and trusted networks for context-aware access.
Govern office, VPN, cloud, partner, and remote-work network trust with scope and overlap analysis.
Groups applications into trust zones and limits blast radius through segmentation and dependency awareness.
Applies DLP, clipboard controls, print restrictions, upload controls, watermarking, and regulated-data protections.
Controls AI agents, model providers, shadow AI, prompts, tools, human approvals, and audit requirements.
Manages API inventory, key lifecycle, OAuth posture, rate limits, service identities, and runtime telemetry.
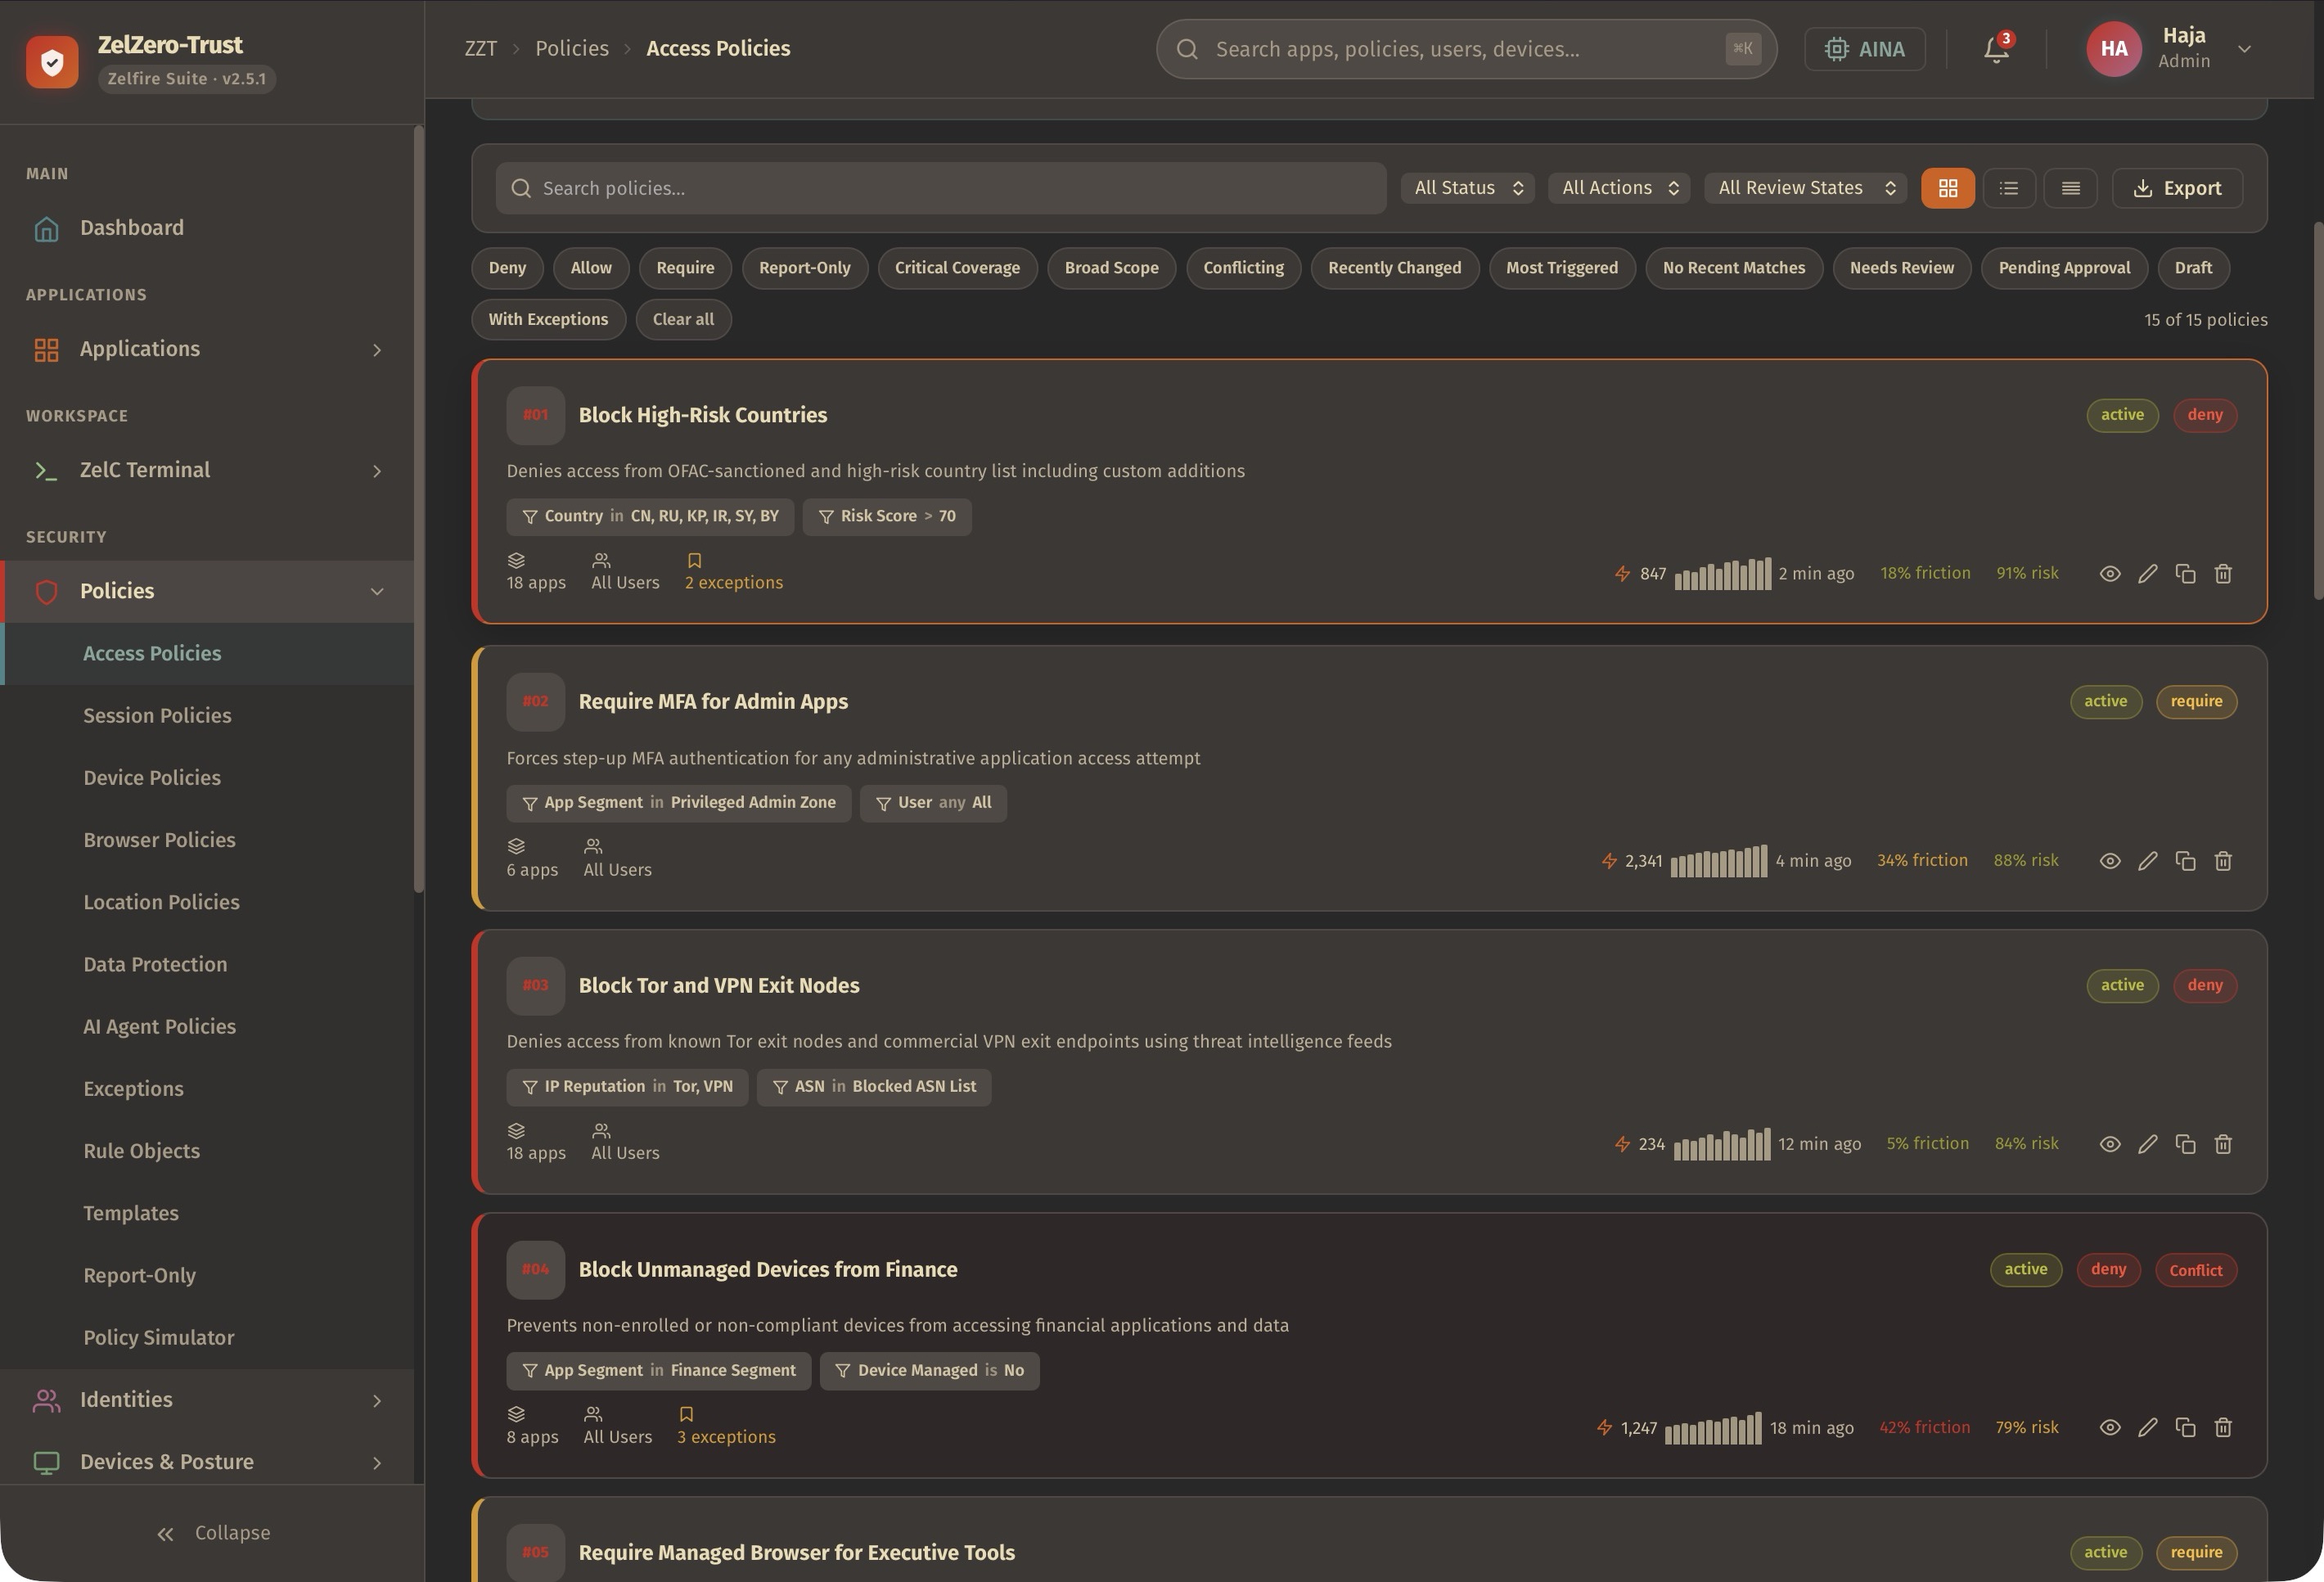
Supports allow, deny, monitor, step-up MFA, browser-only, isolation, report-only, and simulation workflows.
Explains matched policies, failed conditions, rule objects, exceptions, friction, and blast-radius estimates.
Tests risky policy ideas safely before enforcement with readiness scoring and false-positive analysis.
Tracks posture gaps, scripts, approvals, campaigns, rollback readiness, and time-to-resolution analytics.
Shows overall posture scores, criteria-level failures, department comparisons, and remediation prioritization.
Tracks issuance, renewal, revocation, chain health, device identity, and mTLS readiness.
Supports SAML, OIDC, SCIM, JIT provisioning, group push, mapping validation, and sync health analysis.
Tracks enrollment, method strength, recovery gaps, campaign progress, and privileged-user assurance.
Provides charts, heatmaps, comparisons, timelines, and All Data views that remain useful long term.
Explains decisions, suggests safer configurations, predicts friction, and highlights cleanup opportunities.
Includes a security-native coding and simulation workspace with templates, query generation, and execution traces.
Built for strict tenant isolation across apps, users, devices, logs, analytics, and workflows.
ZelZero-Trust combines application security, identity governance, device trust, network intelligence, data protection, AI governance, analytics, and simulation into one operational platform.
Policy control, least privilege, segmentation, remediation, and reporting in a single workflow.
Reviews, certification, external identity governance, posture scoring, and audit-ready evidence.
INSIDE ZELZERO-TRUST
Explore 13 product screenshots. Select any image for a closer look.
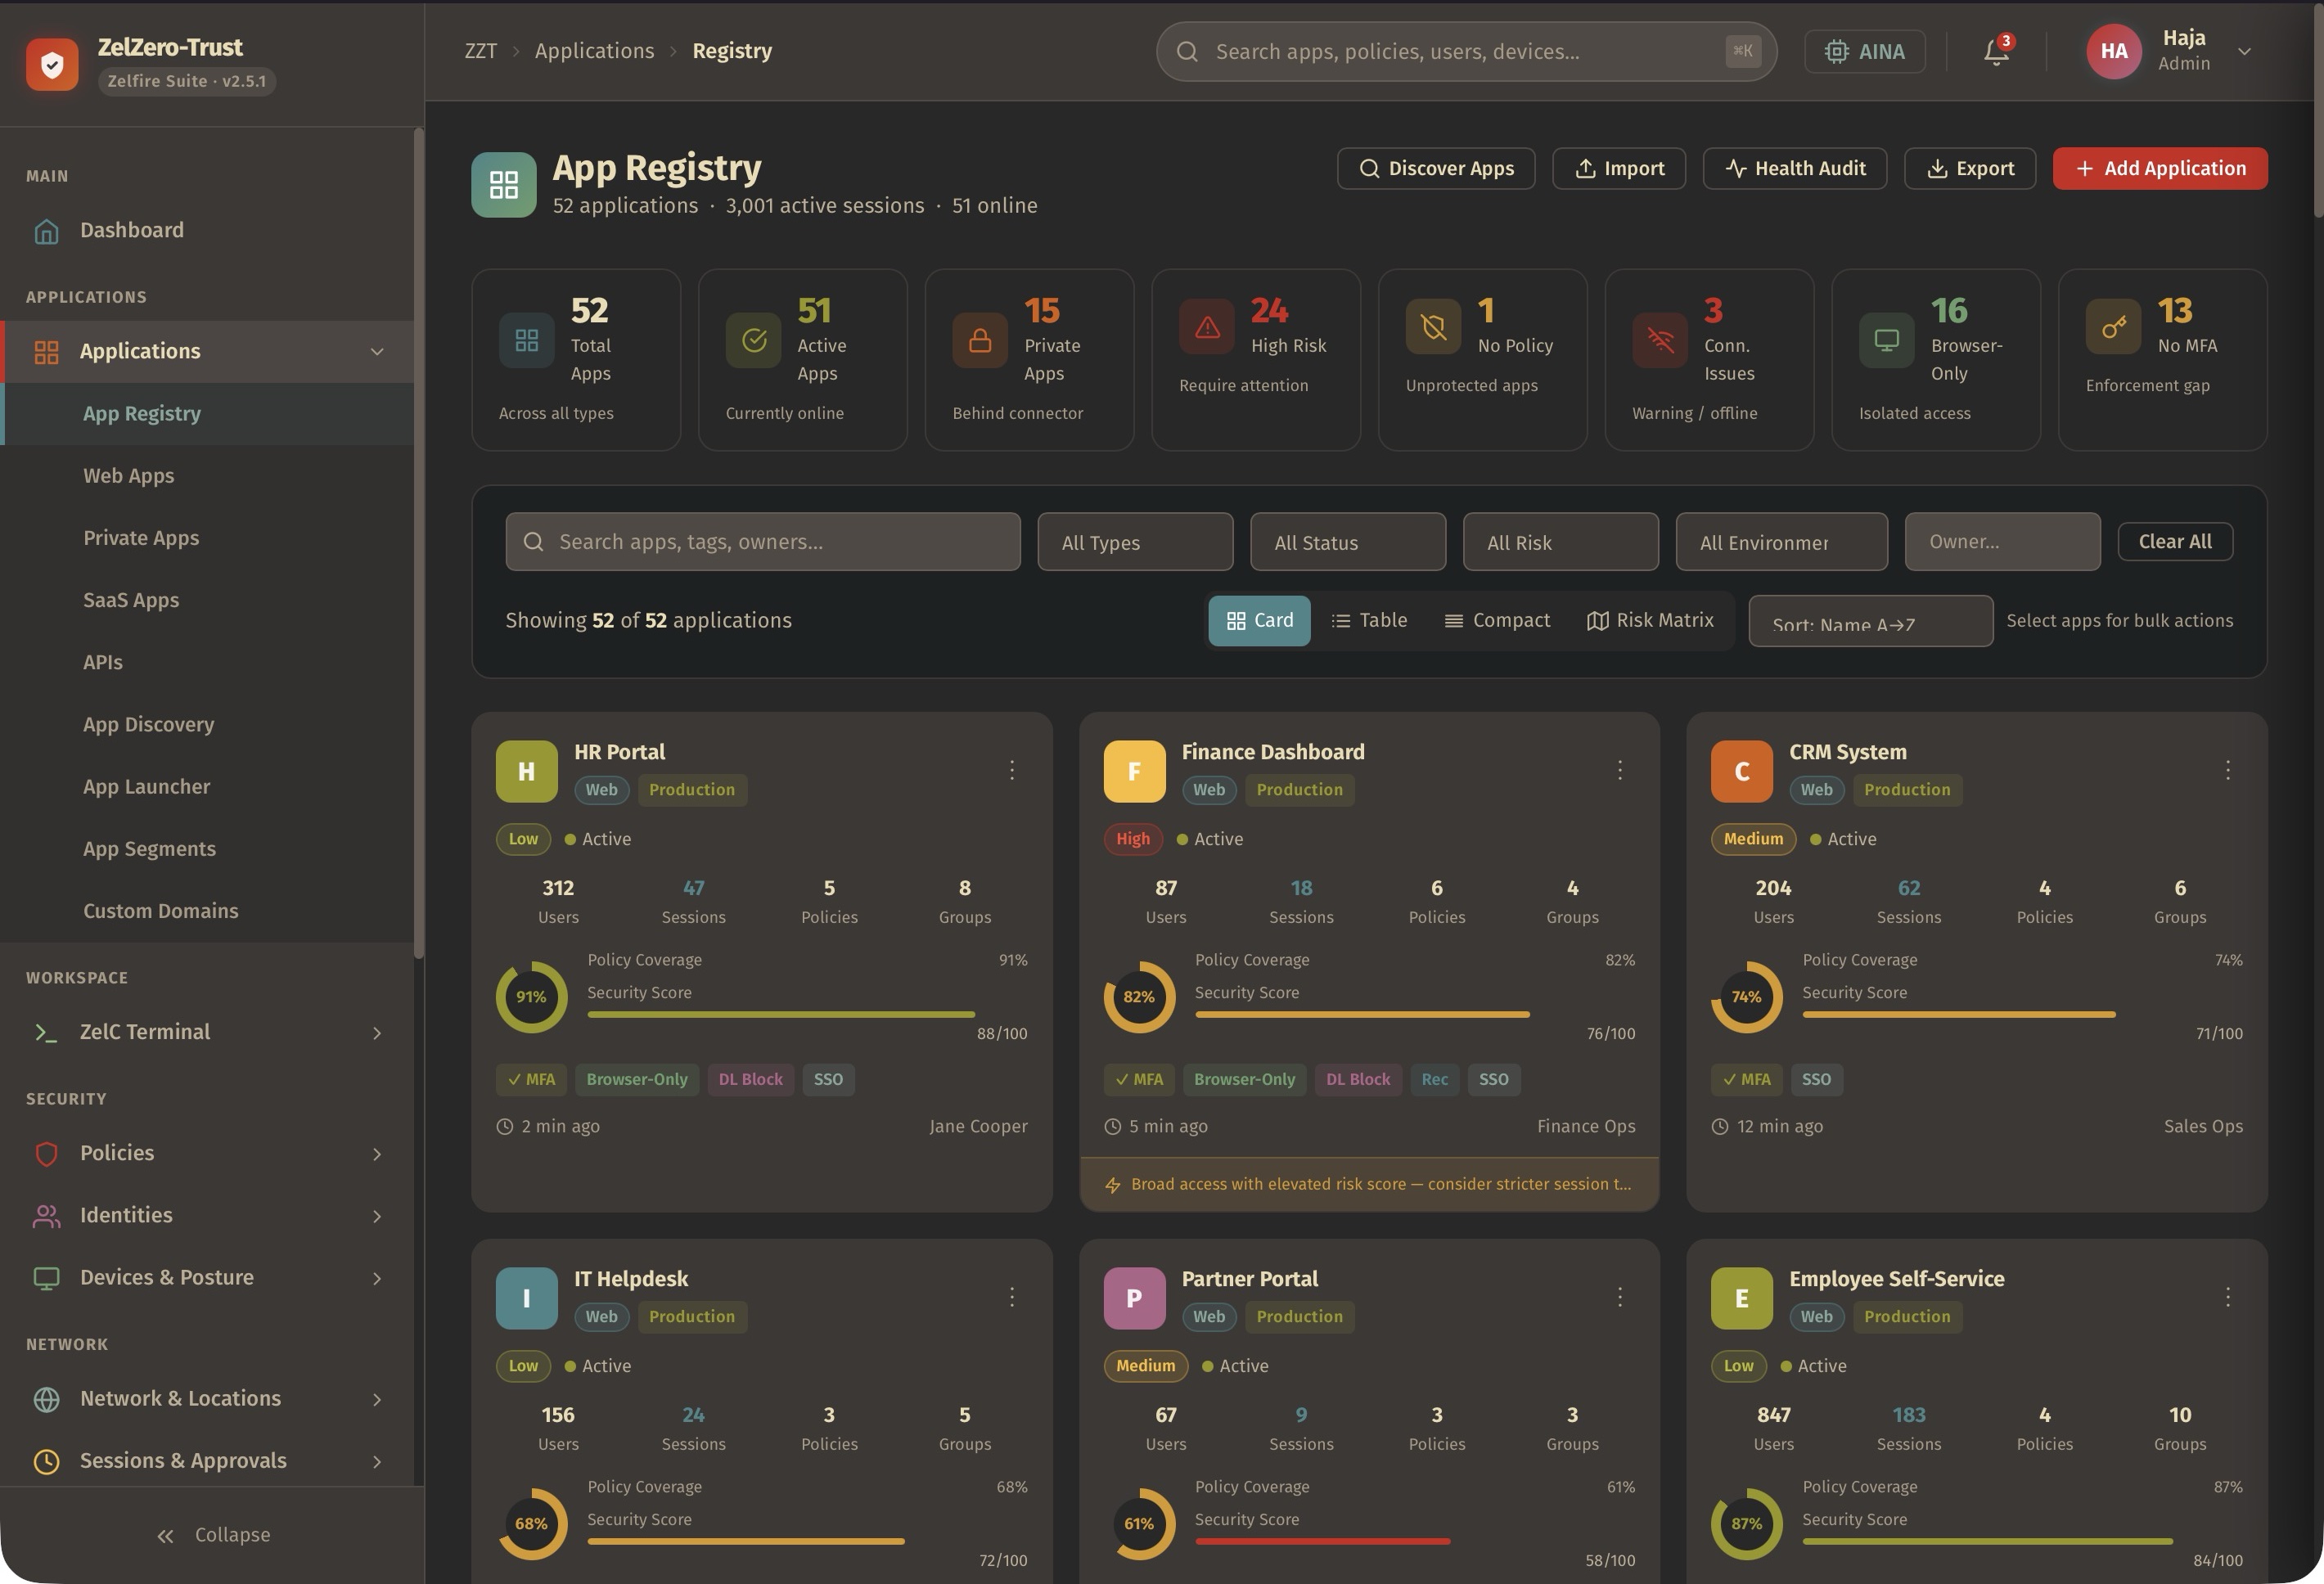
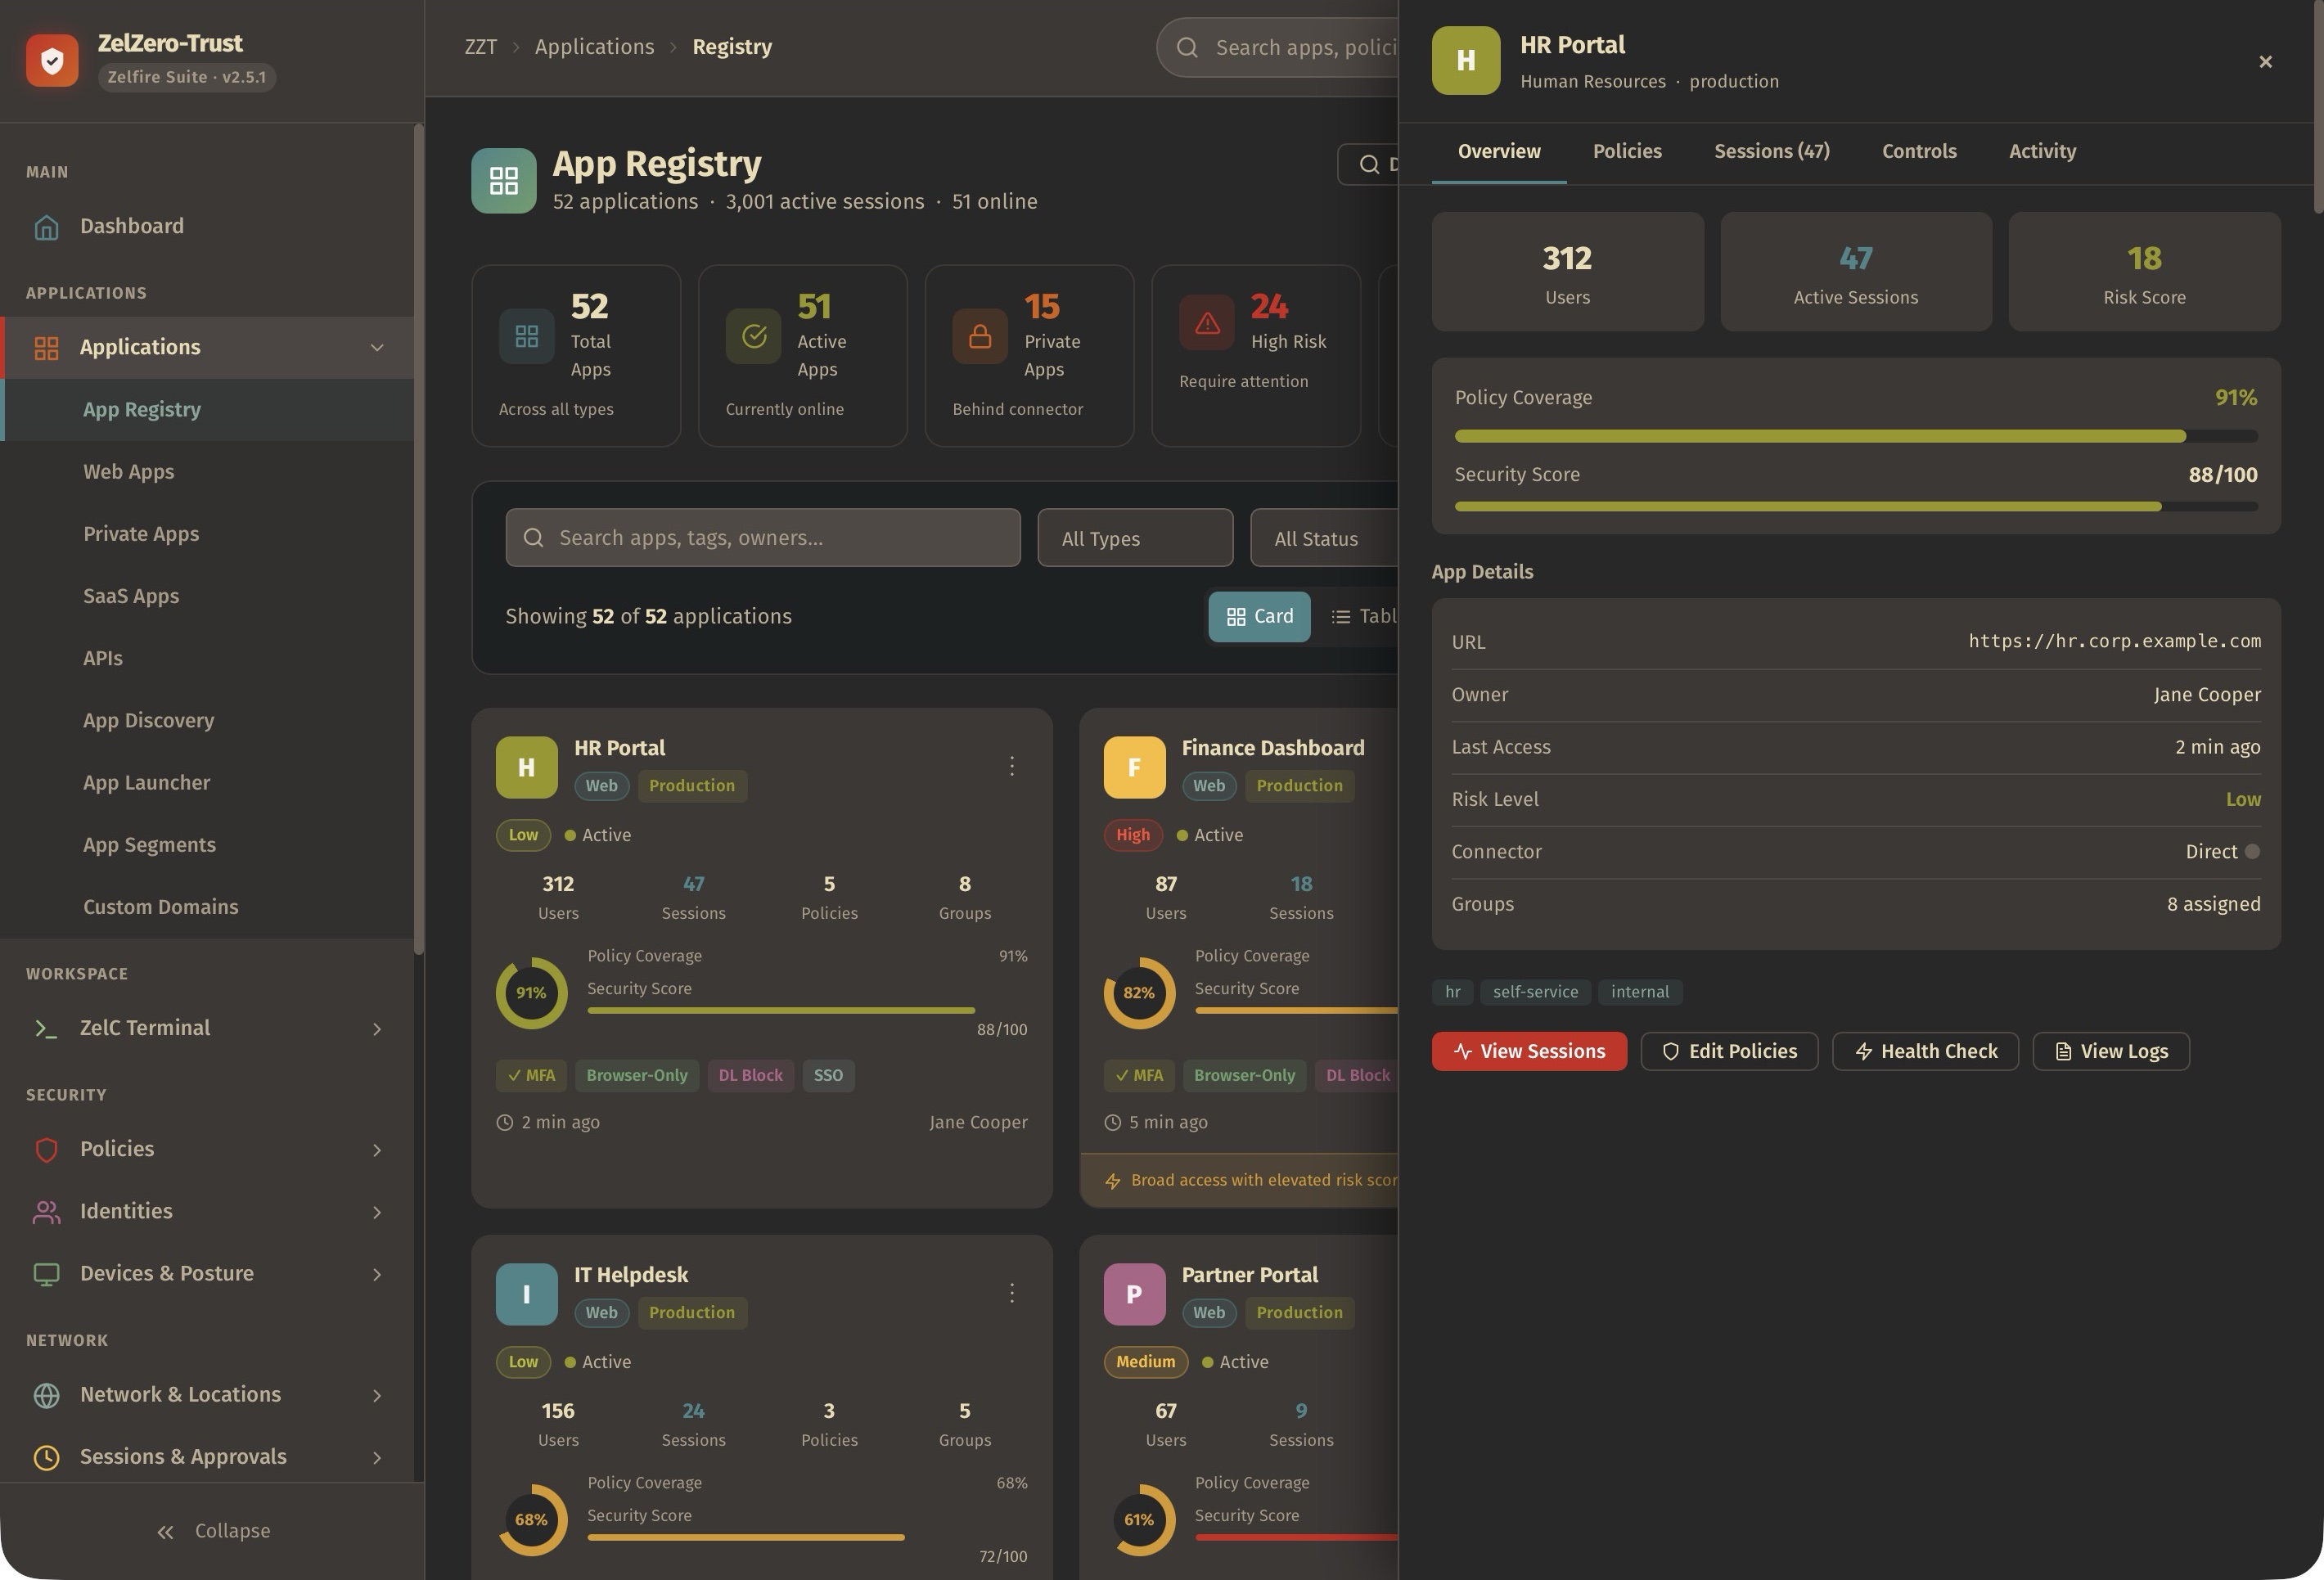
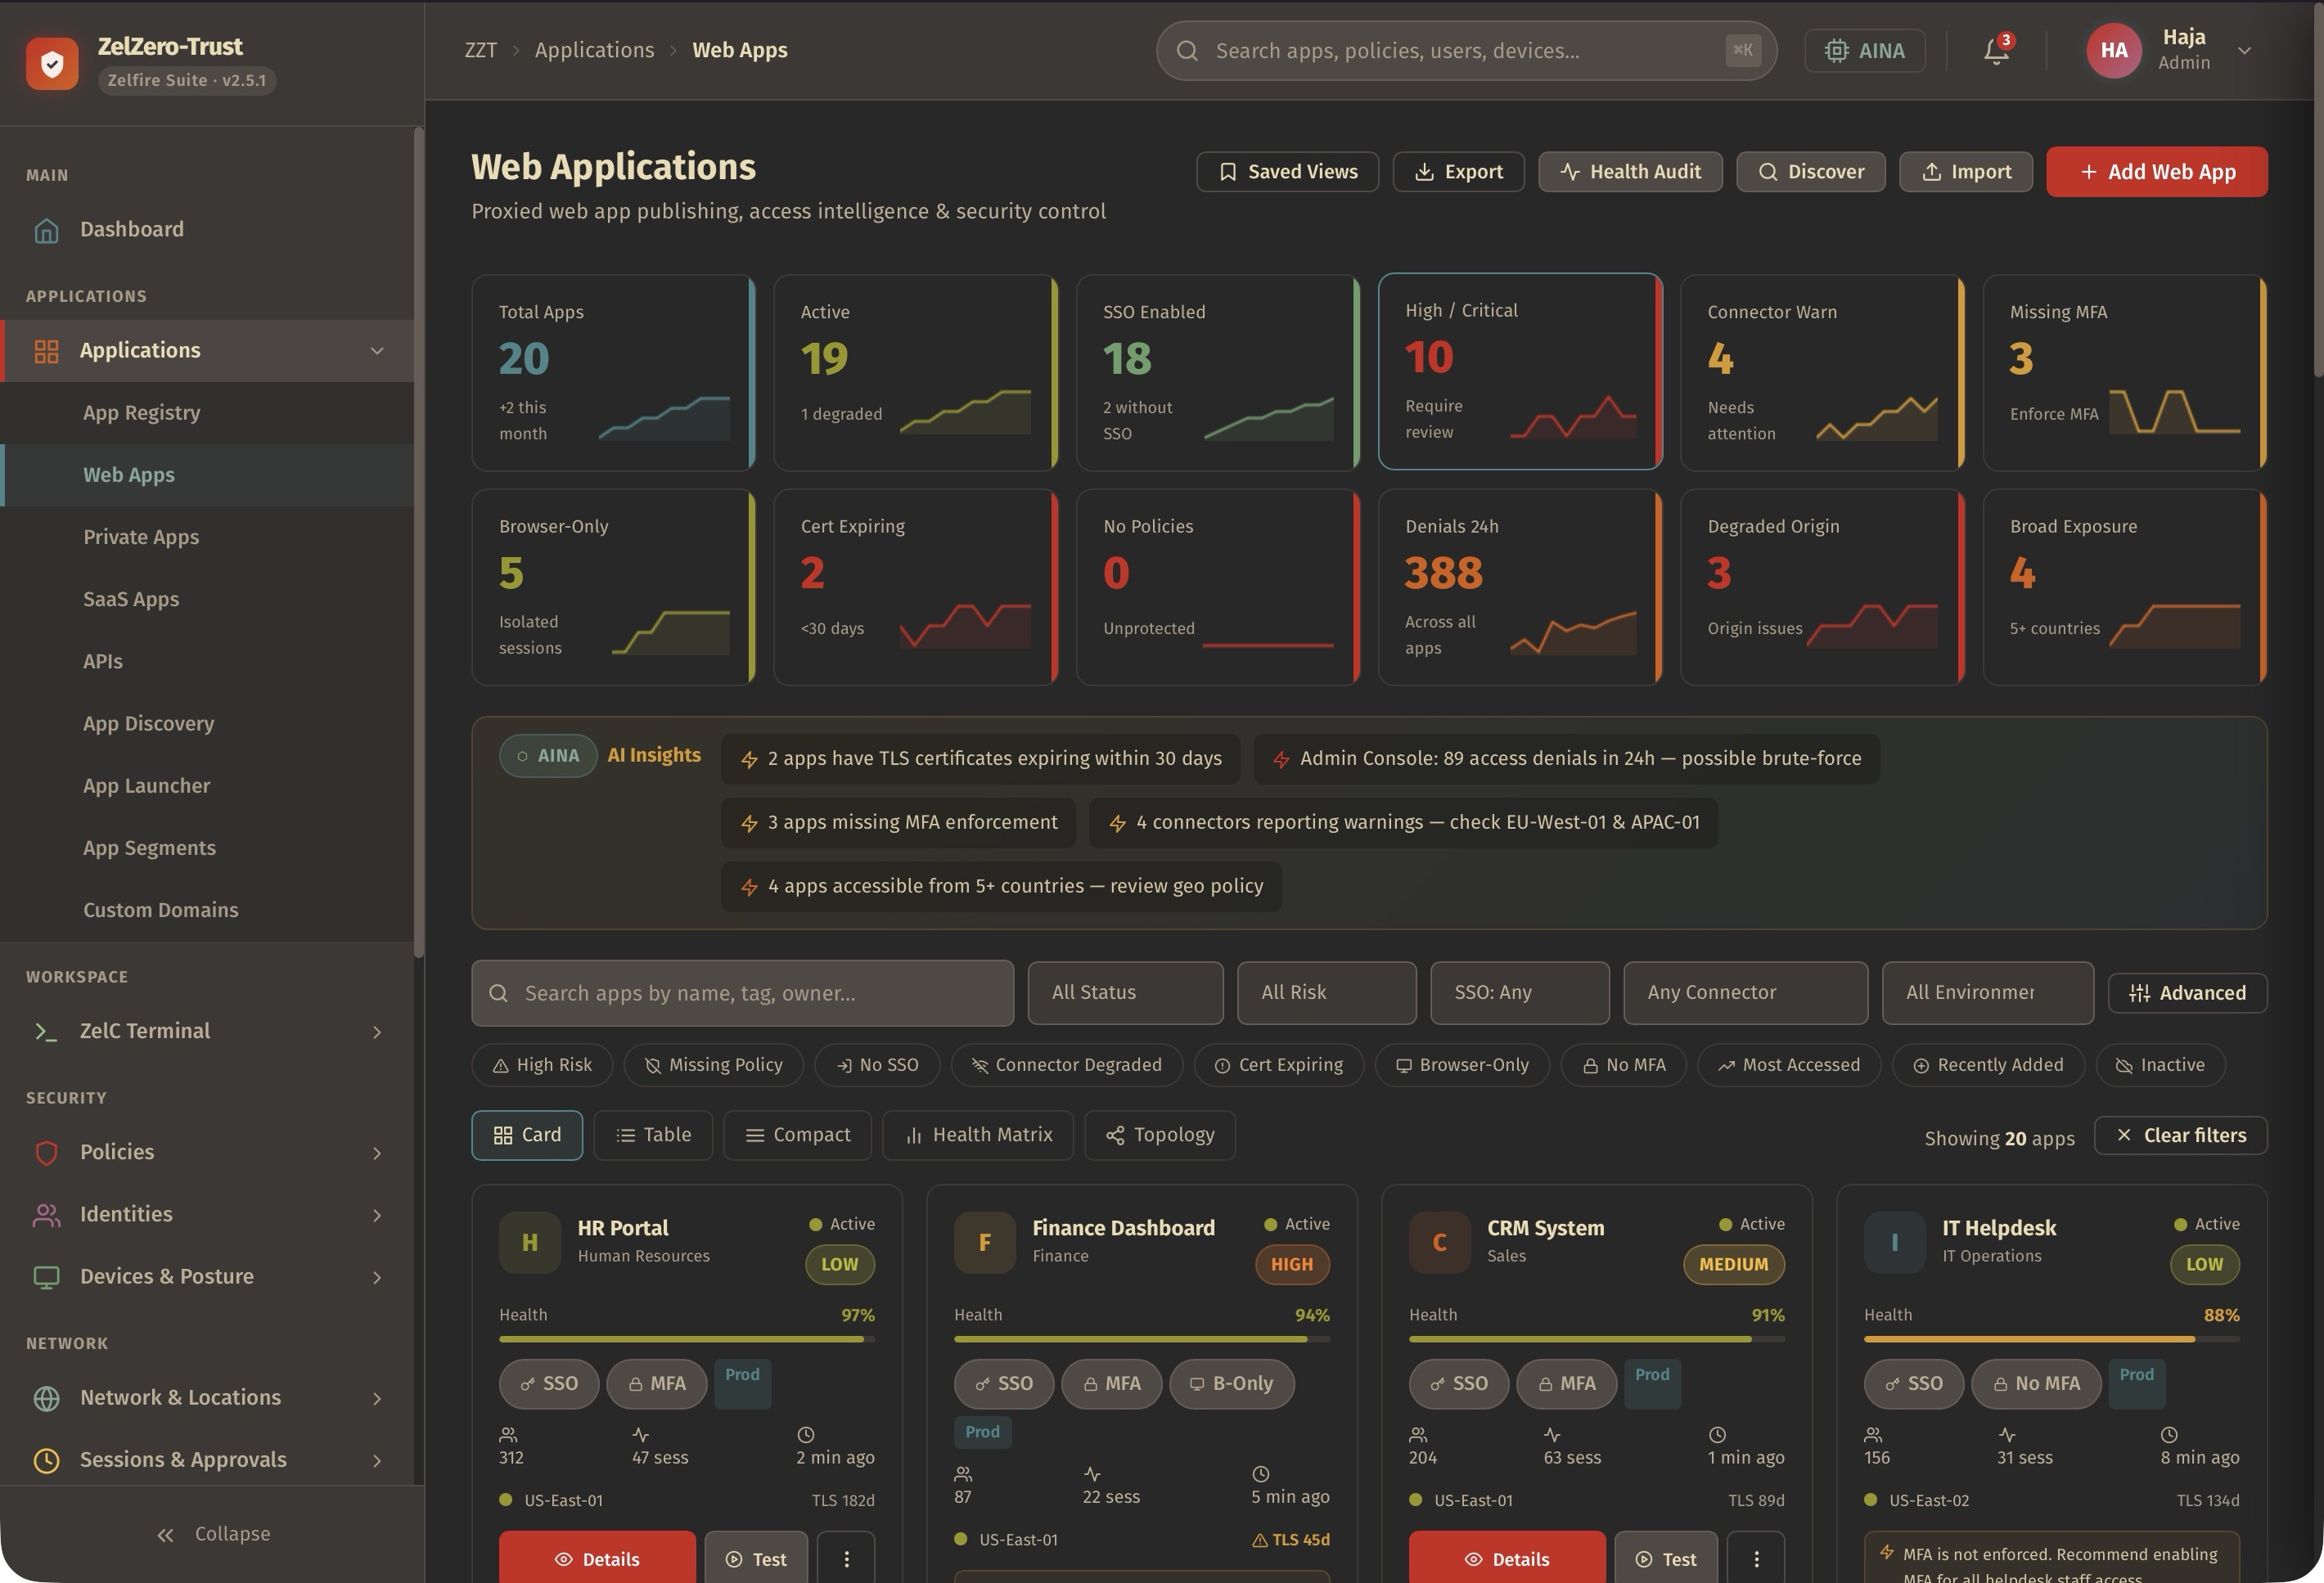
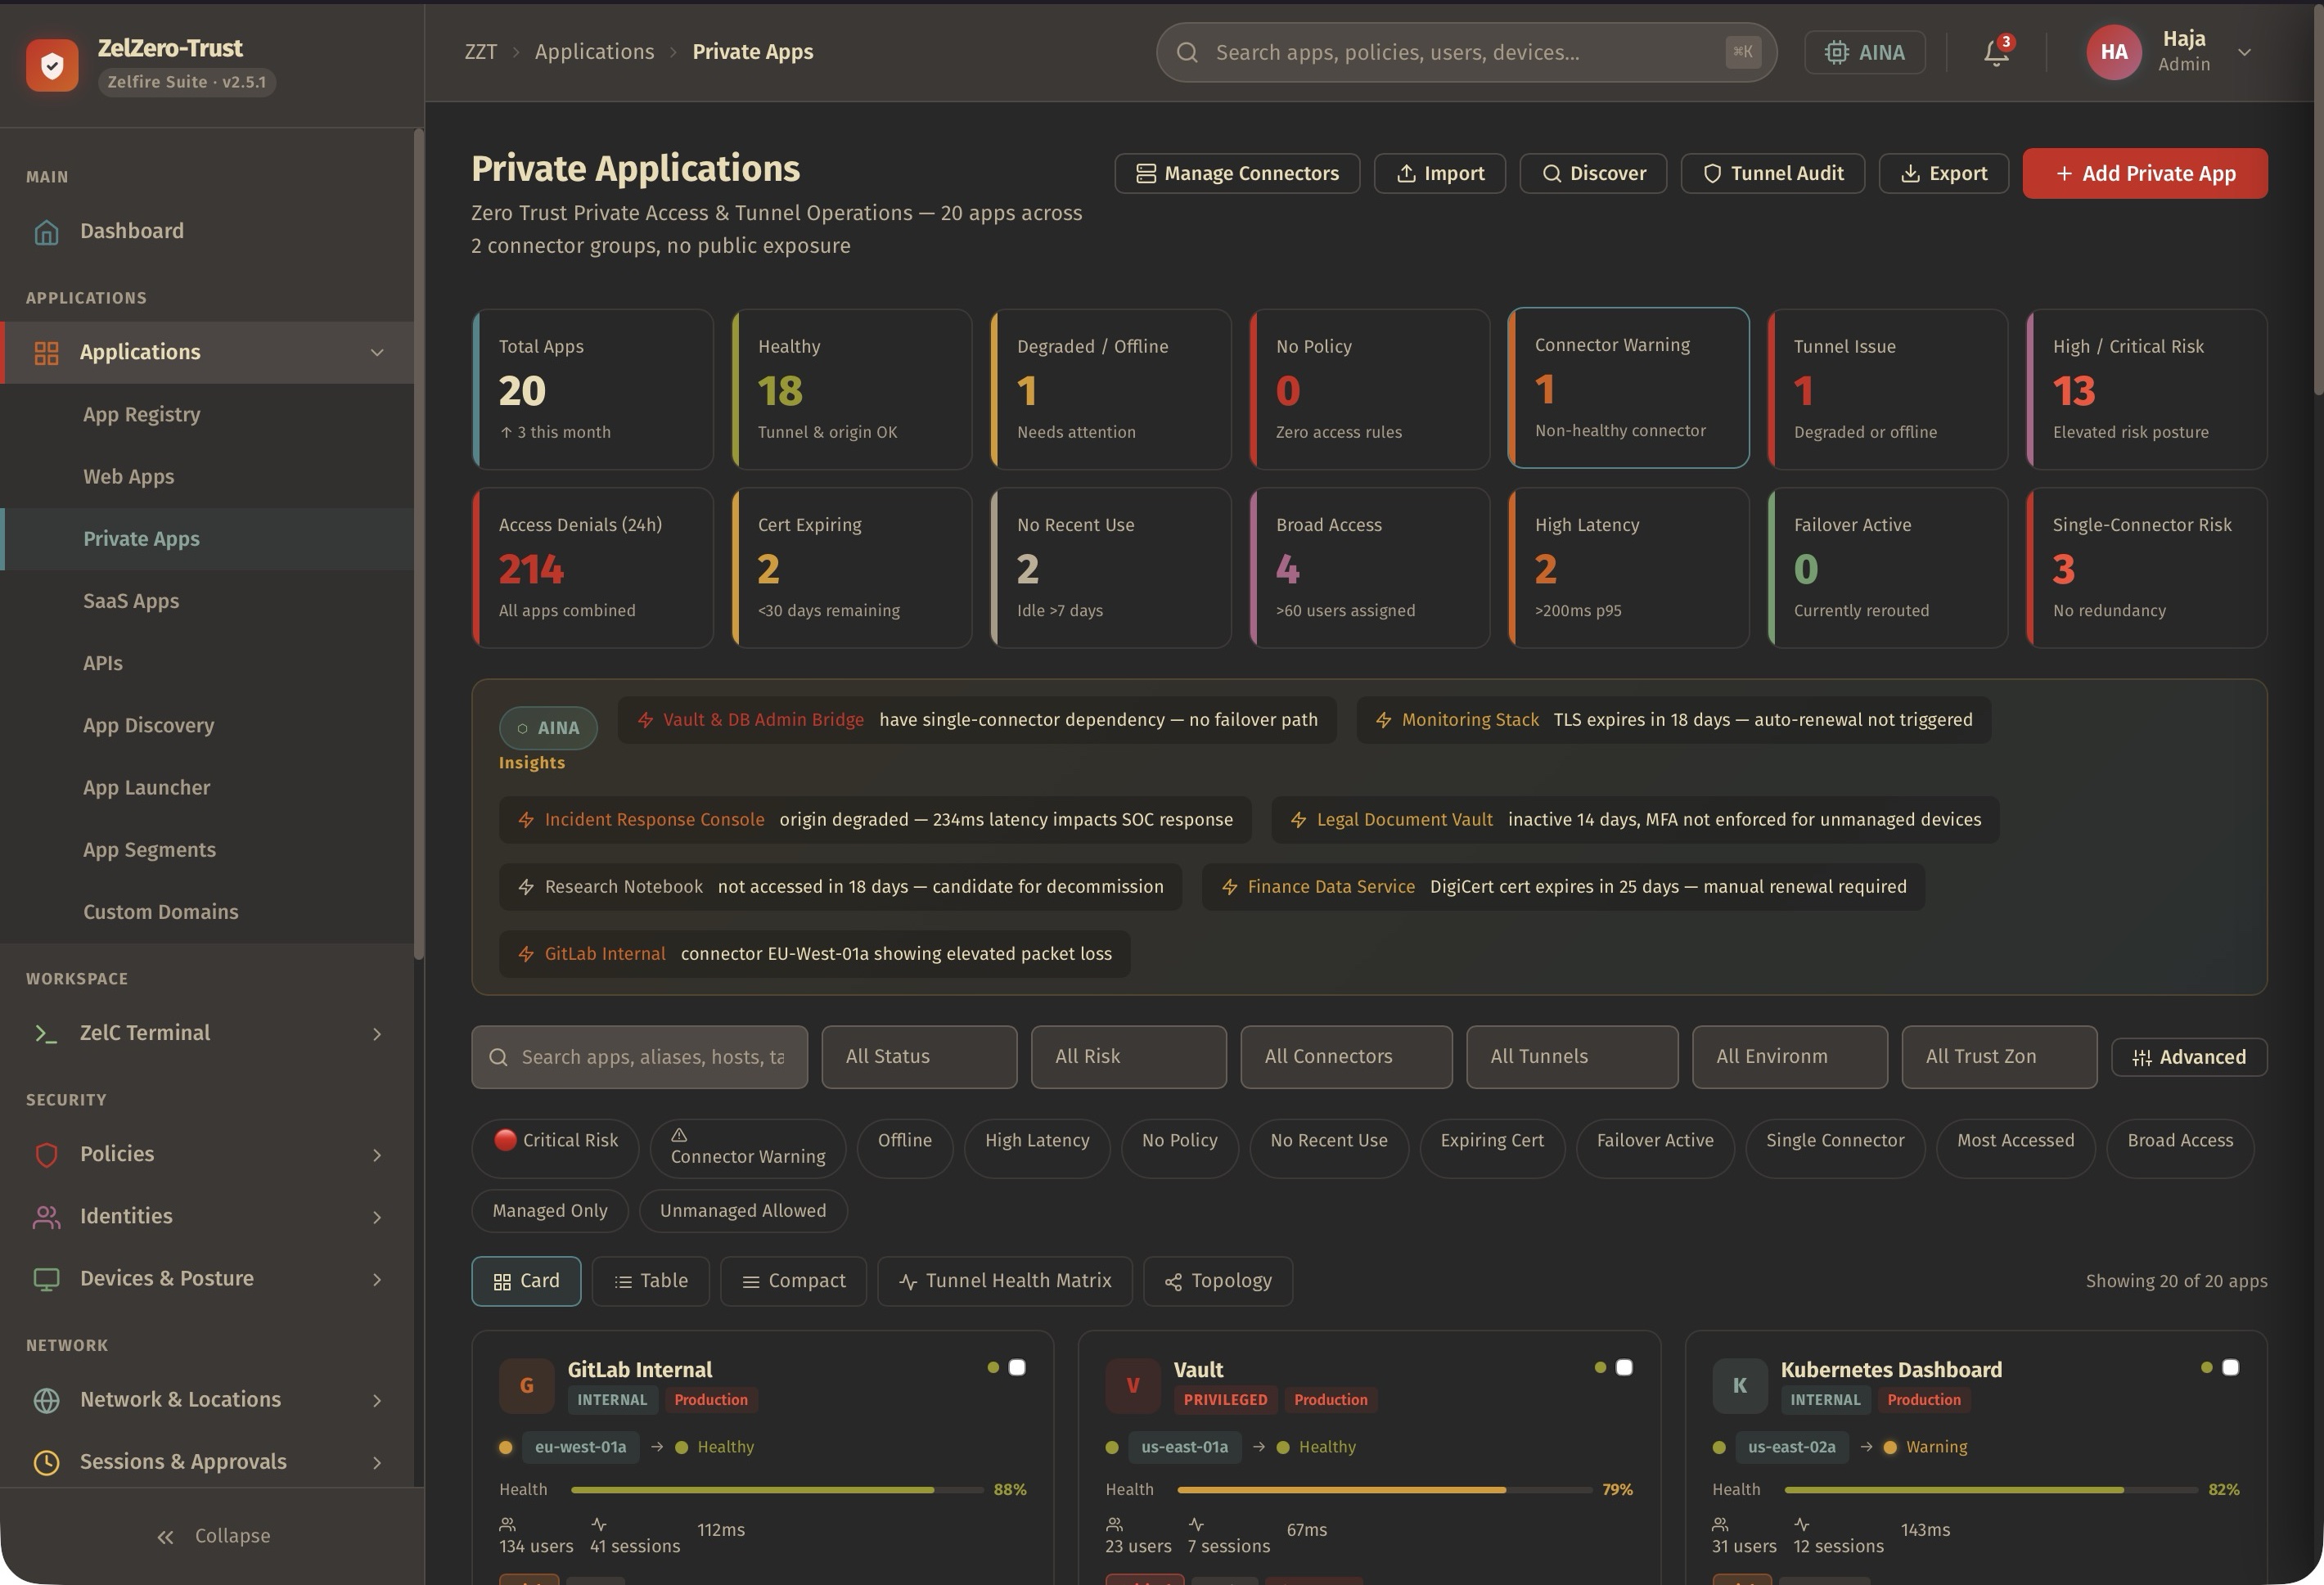
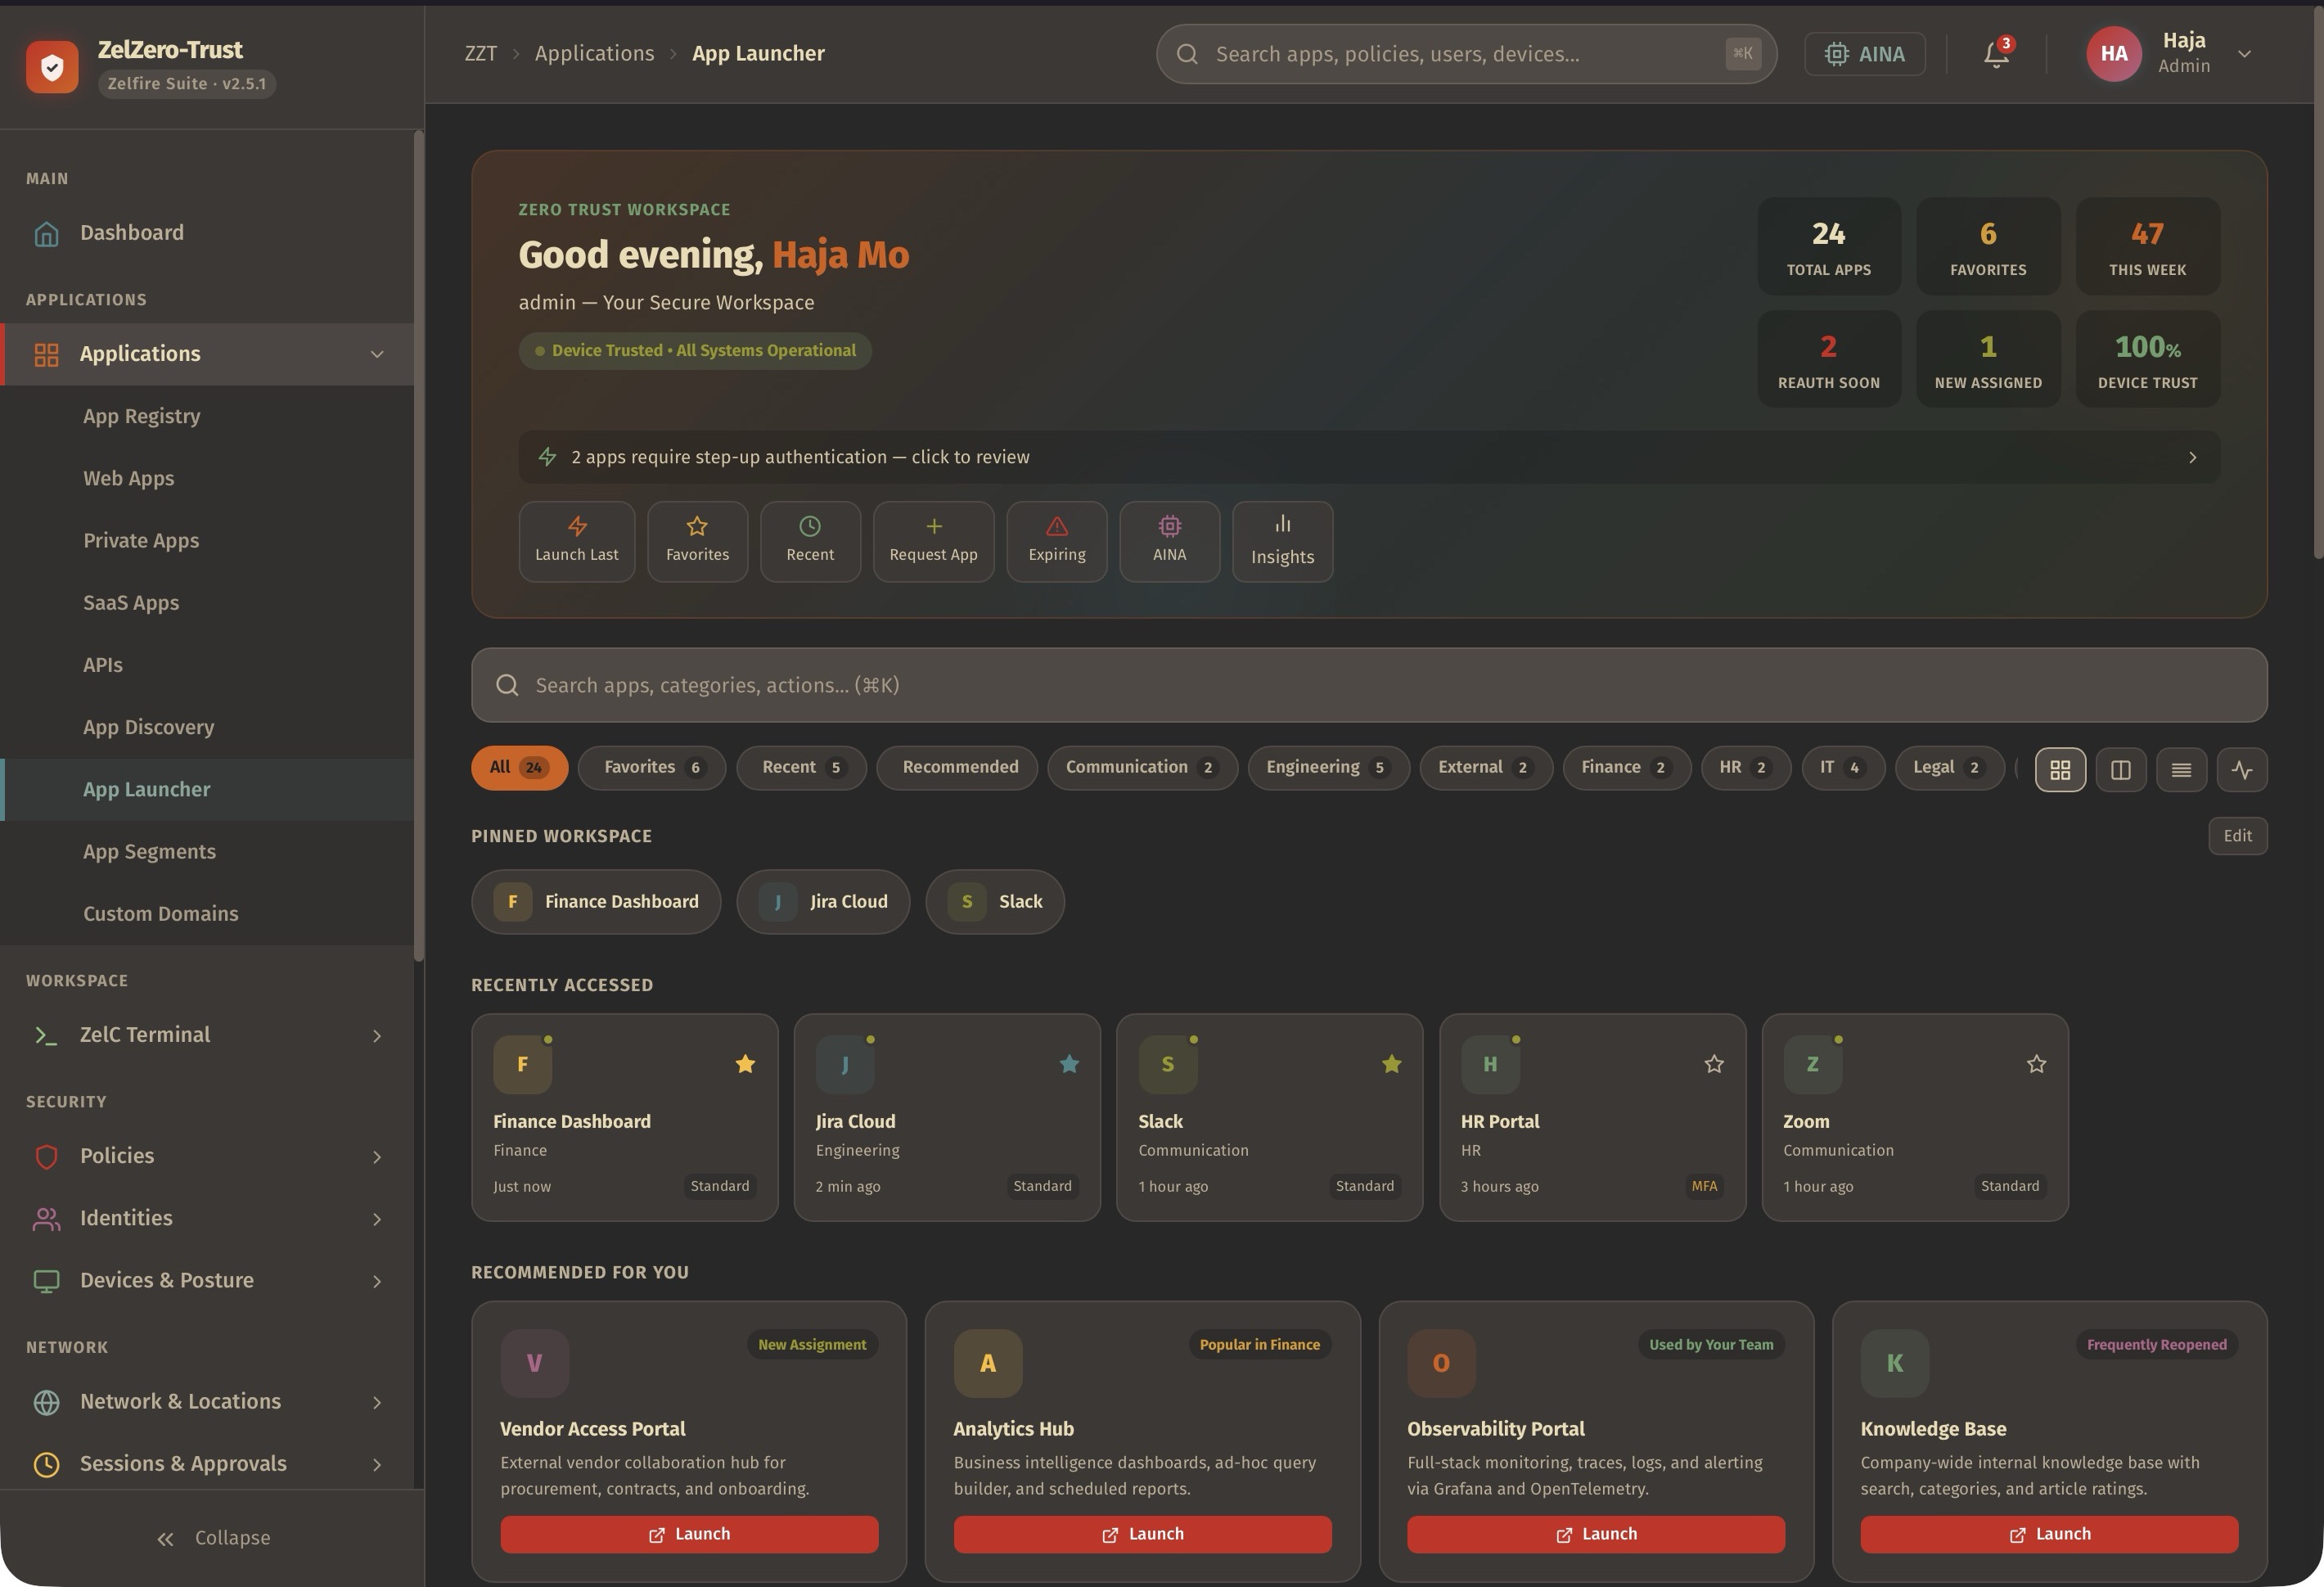
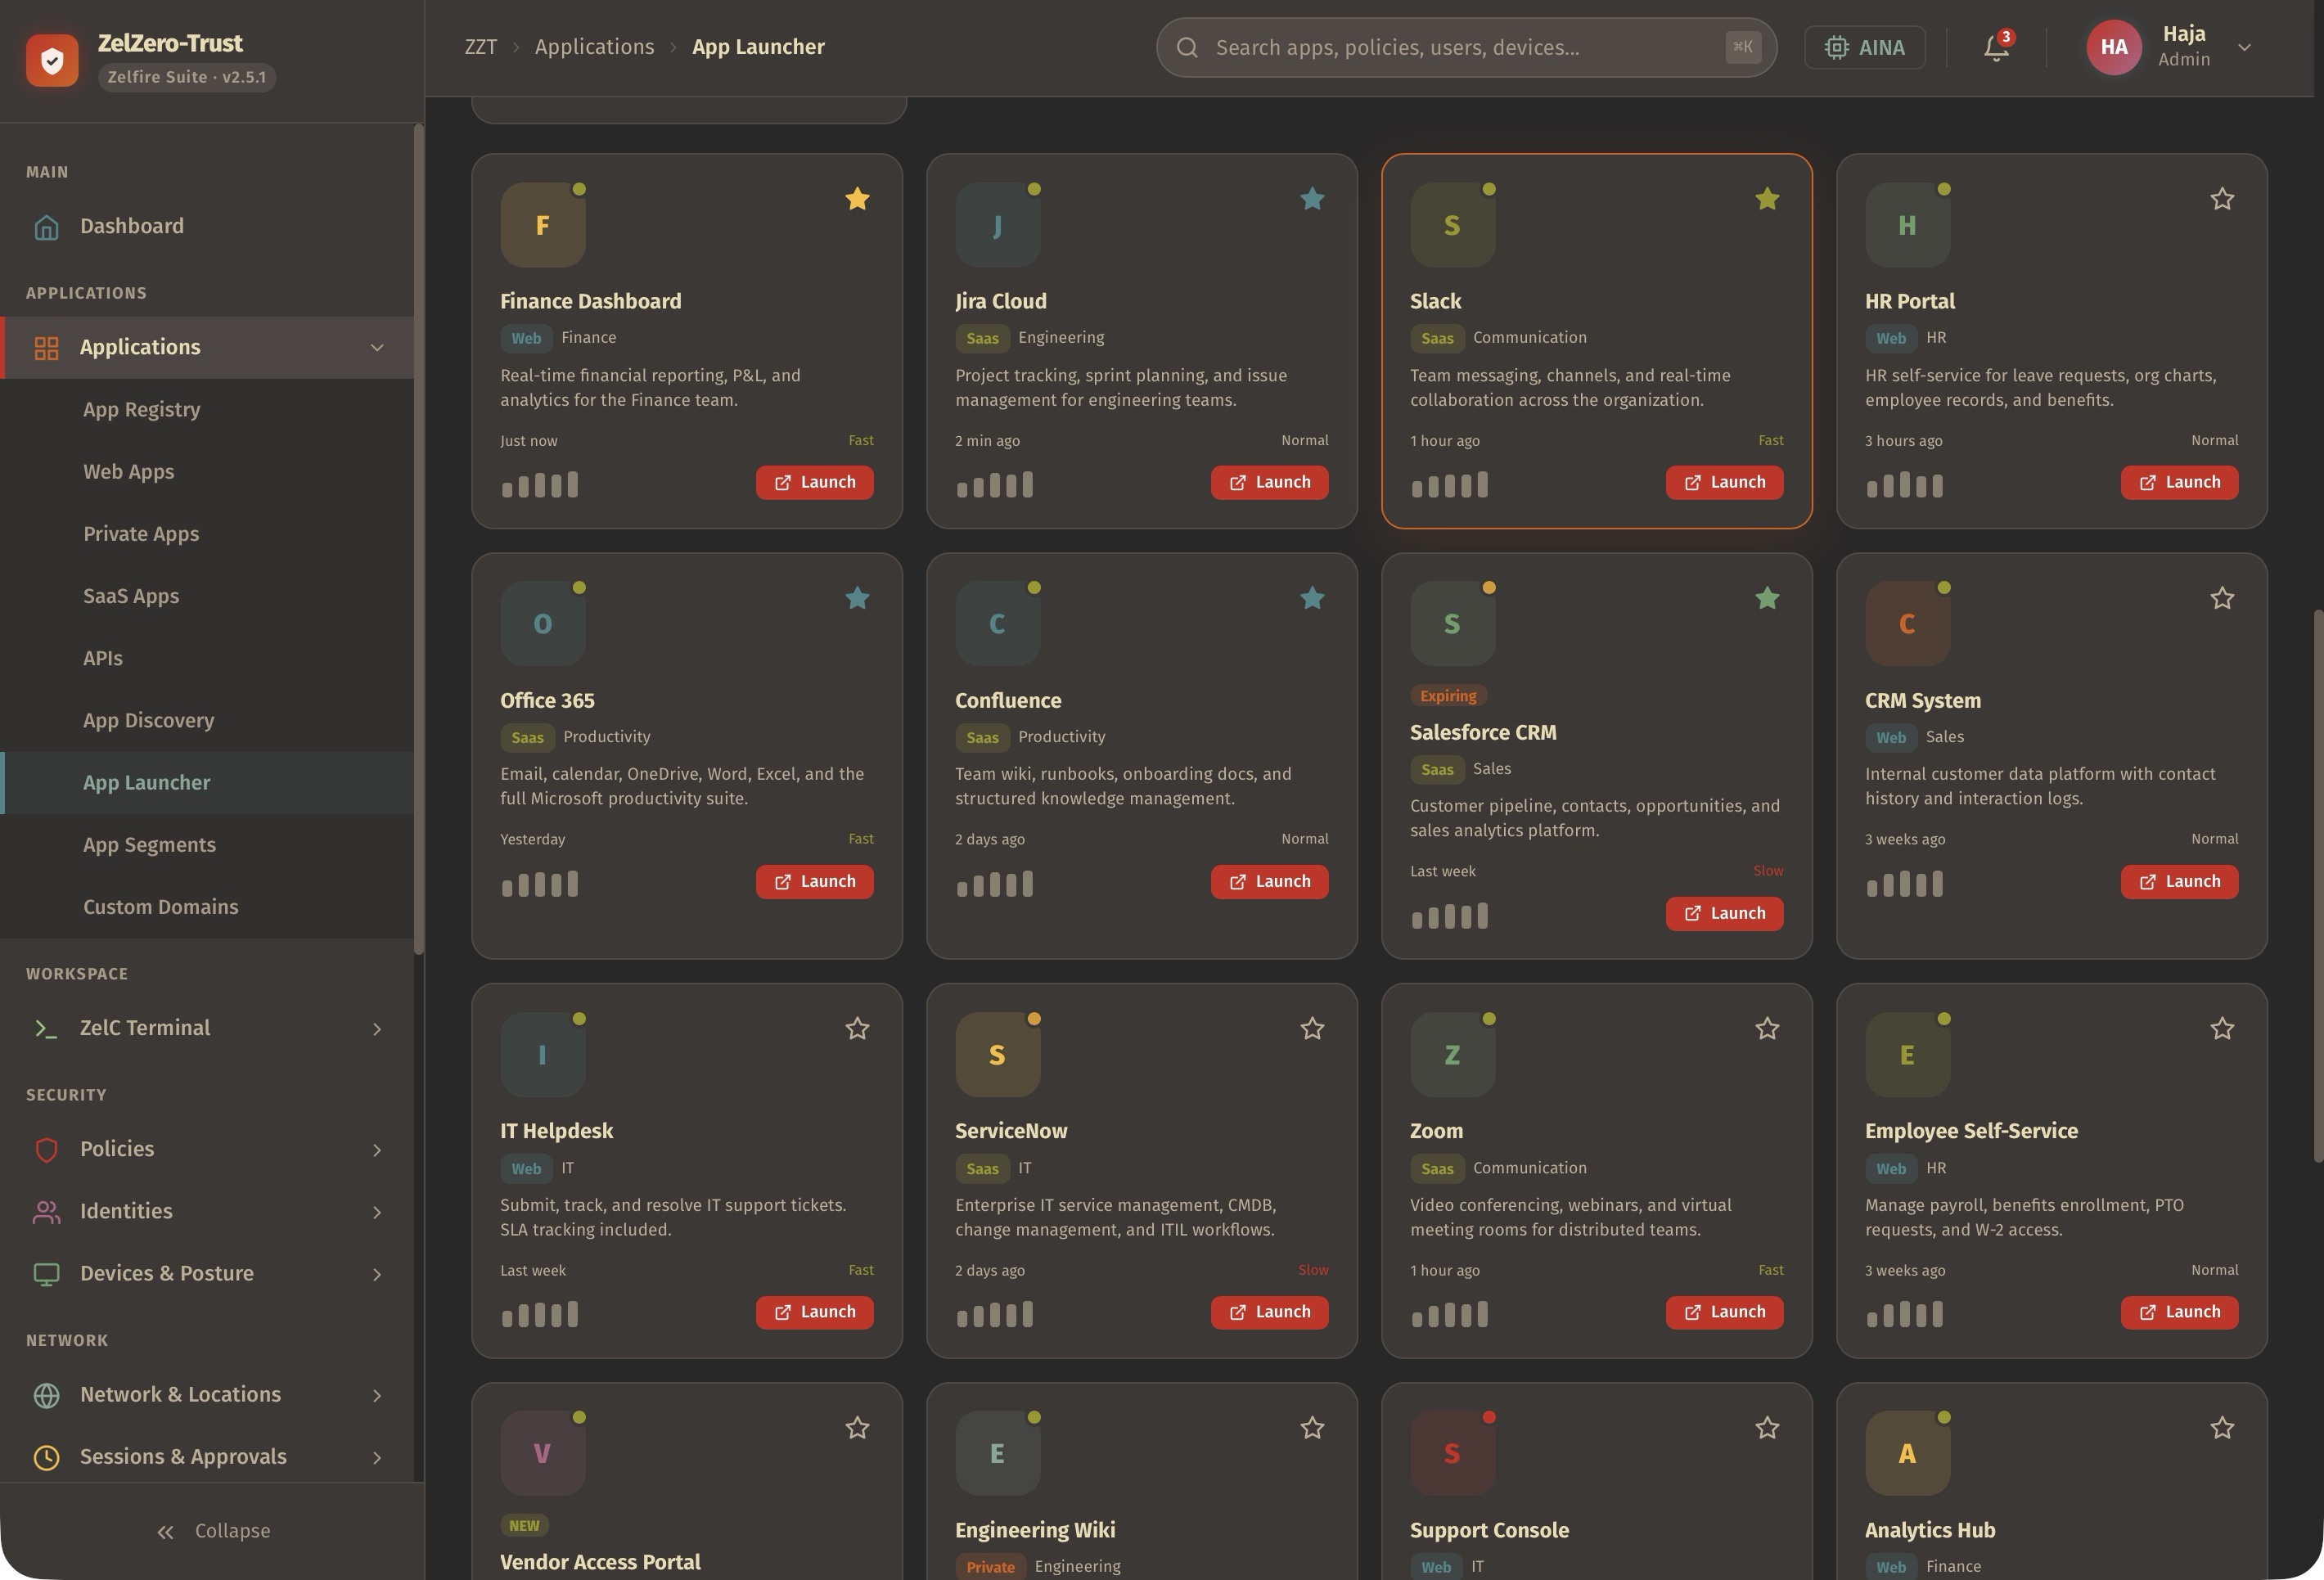
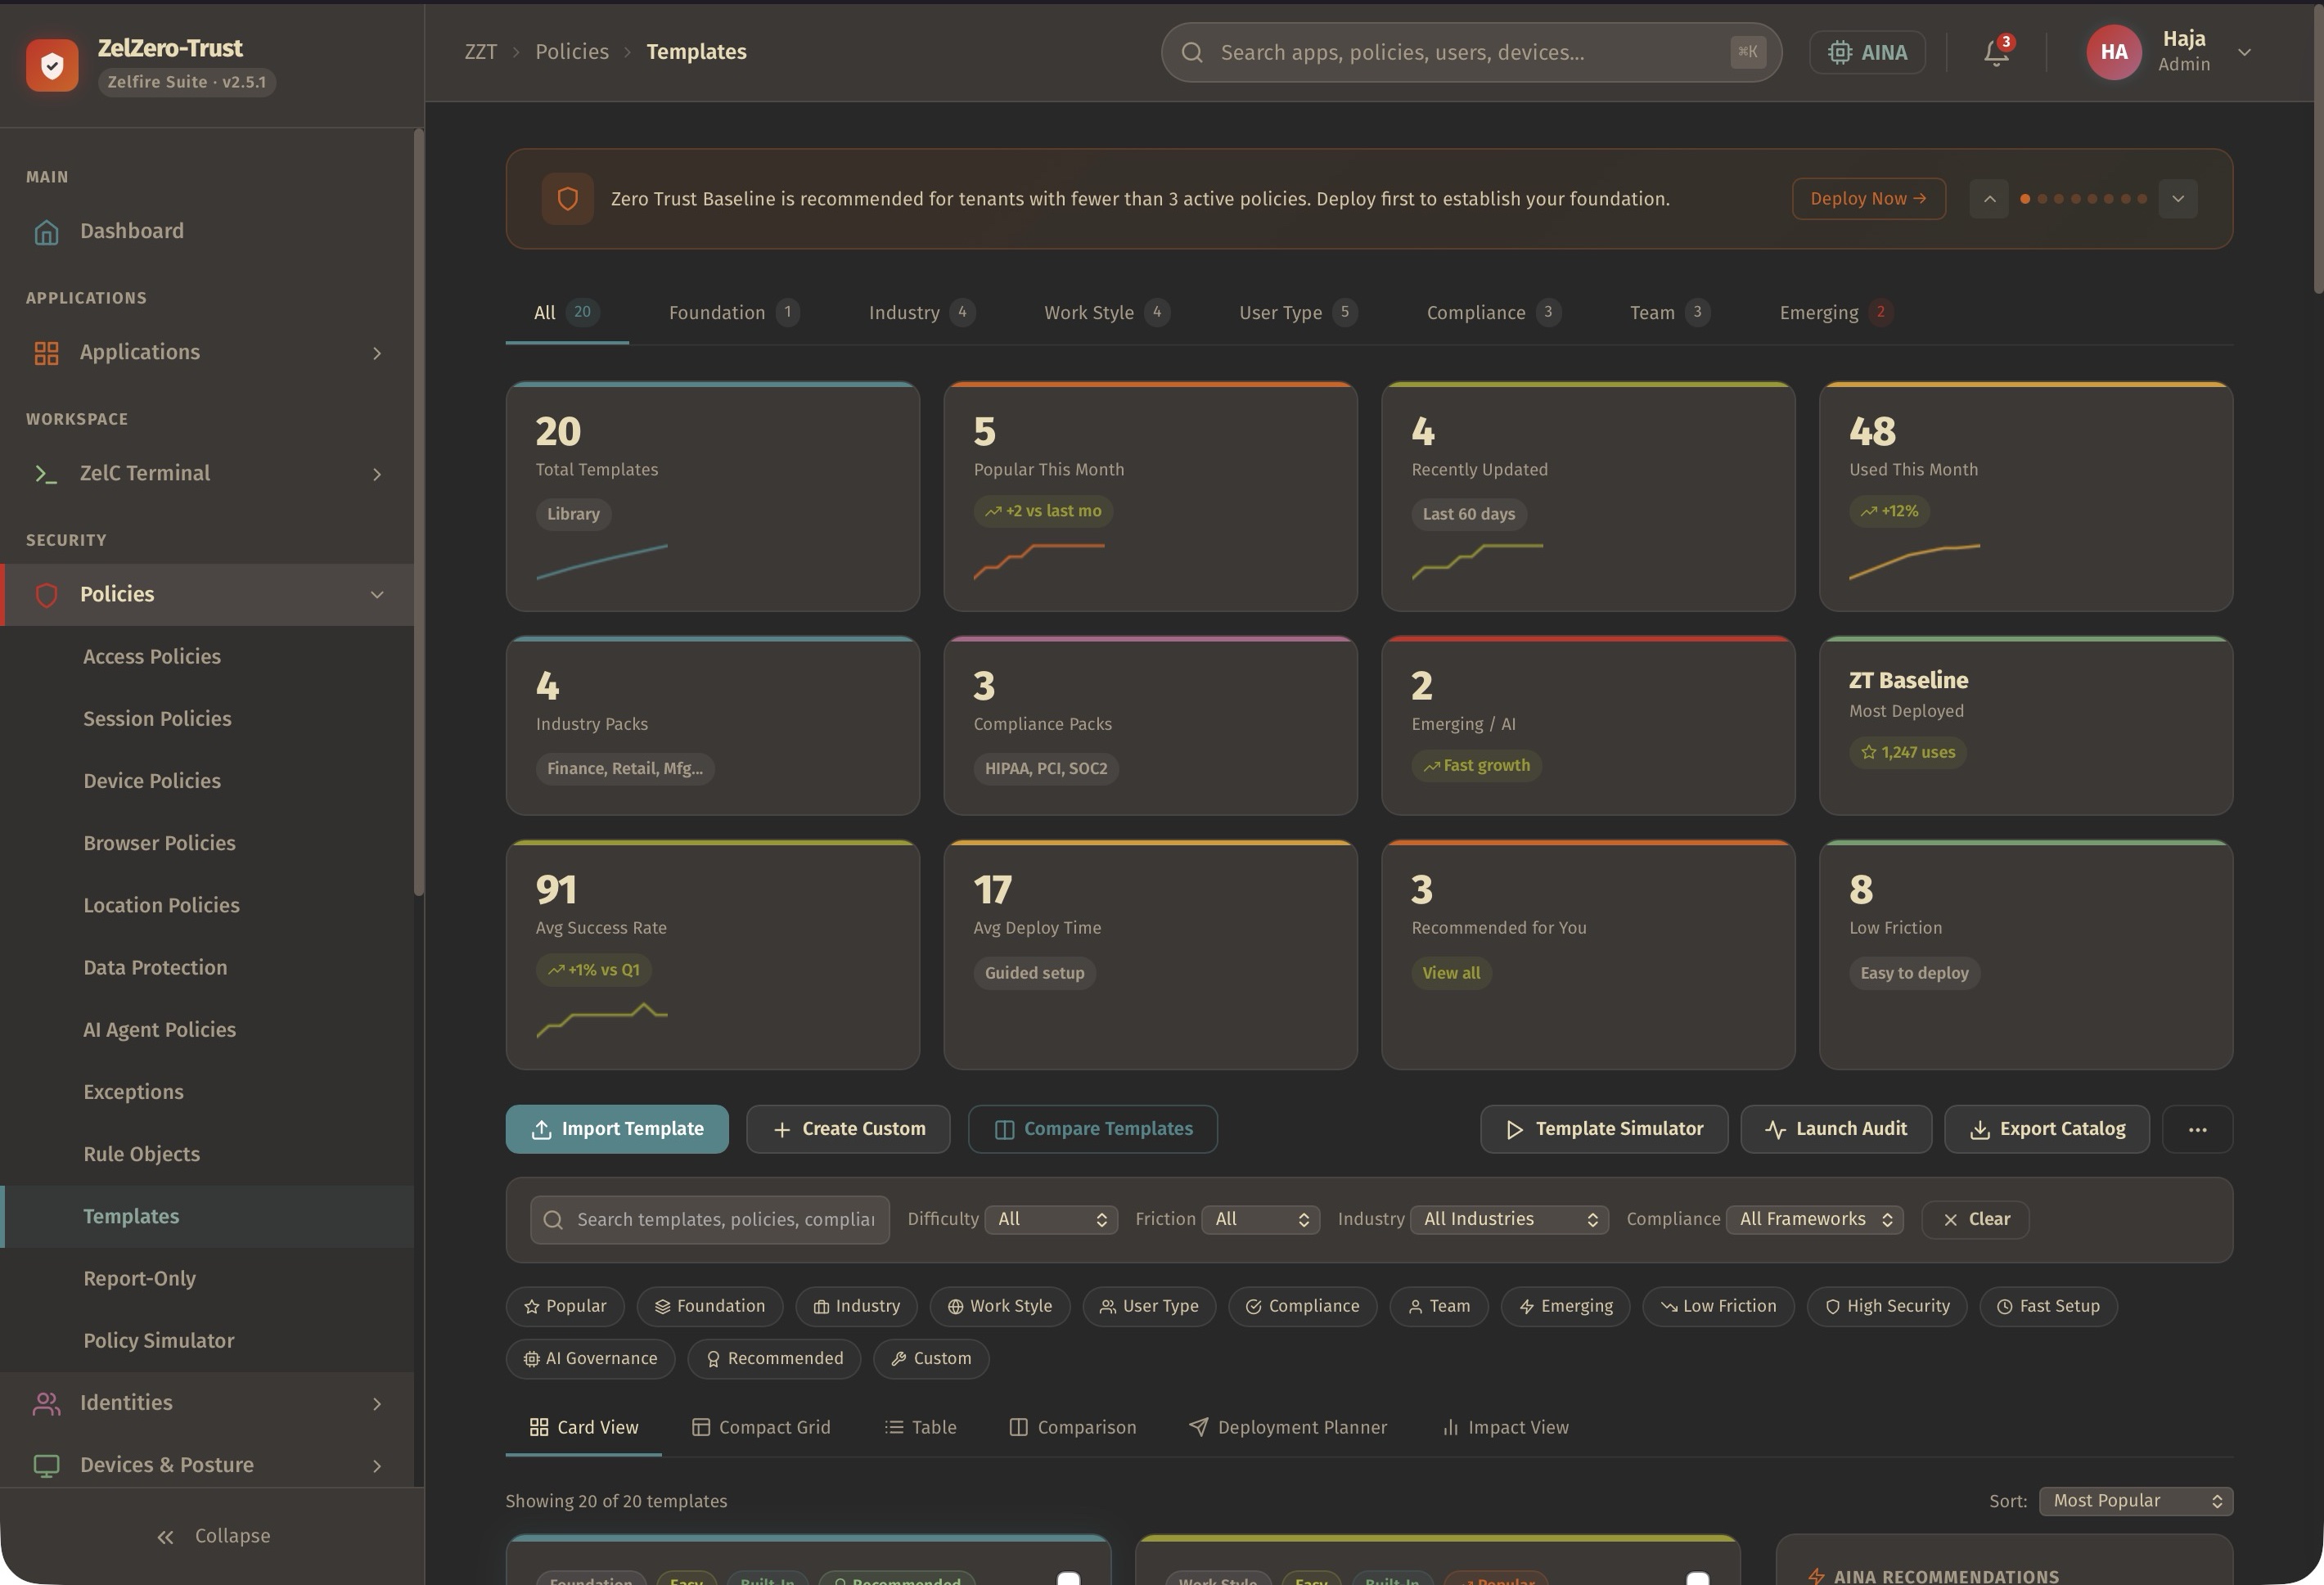
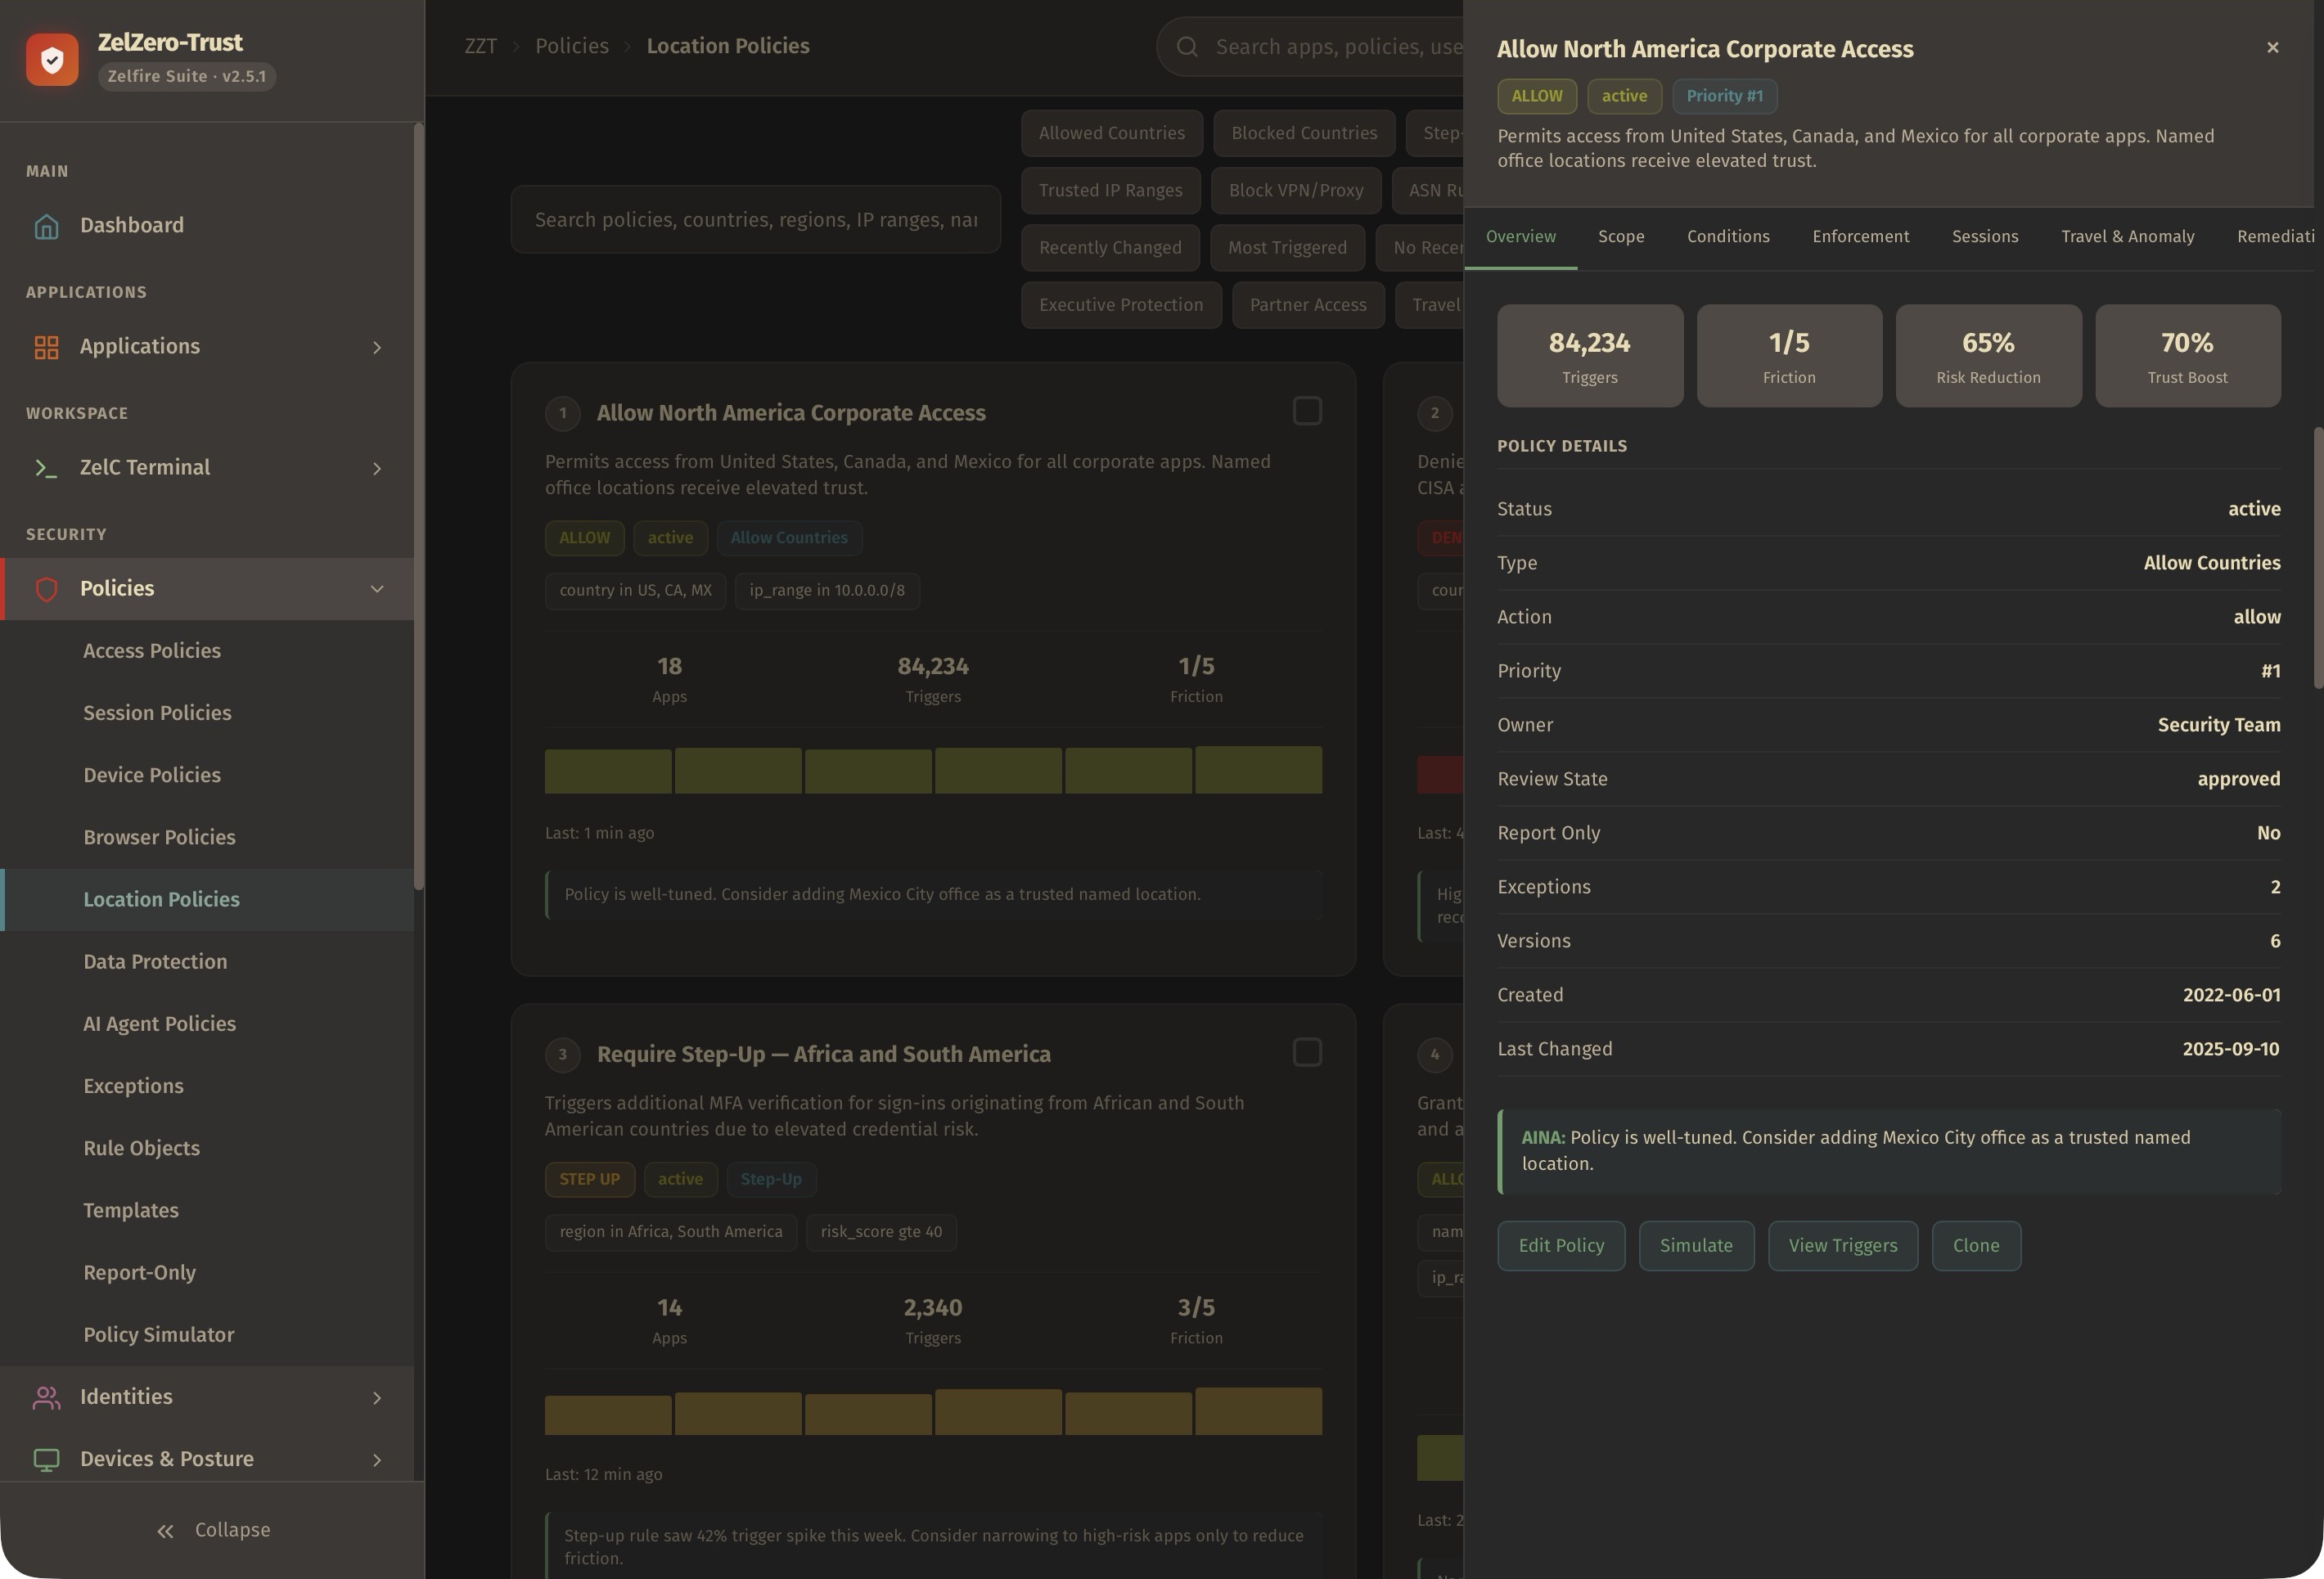
THE DETAILS THAT MATTER
Answers about the product, its capabilities, and how it fits into your security workflow.
No matching questions. Try another word or clear the search.
Explore how AINA connects intelligence across Zelfire, and find the products that complement your workflow.
Web application firewall
Protect web applications with a lightweight agent and centralized security decisions, without DNS changes.
Cloud security
Connect cloud posture, identity risk, vulnerabilities, and attack paths in one view.
Identity & access
Centralize sign-in, manage identities, and apply consistent access policies.
LET’S CONNECT YOUR DEFENSE
Explore the products, see the workflows, and talk to Rocheston about your security environment.
Request a demo