Intelligence aggregation
Bring threat feeds and environmental signals into one platform.
THREAT INTELLIGENCE
Put the right threats first.
ZelRank aggregates threat intelligence feeds, environmental signals, and risk indicators, then ranks them by relevance and impact. AINA helps teams focus on threats that matter to their own environment.
Threat intelligence
BUILT FOR YOUR WORKFLOW
Bring threat feeds and environmental signals into one platform.
Evaluate relevance and impact instead of reviewing indicators in isolation.
Give investigators a prioritized starting point for their work.
THE COMPLETE PRODUCT GUIDE
Get to know the capabilities, workflows, and intelligence behind the product.
Powered by AINA, Rocheston ZelRank is a centralized Cyber Threat Intelligence (CTI) platform within the Zelfire Suite that transforms fragmented threat data into actionable, ecosystem-wide security intelligence.
ZelRank consolidates external threat feeds, premium intelligence sources, internal telemetry, and AI-driven analysis into a single platform. No more disconnected dashboards or siloed threat sources. Everything flows into one unified intelligence layer.
🔥 One platform. One intelligence truth. 🔥
Supports IPs, domains, URLs, hashes, certificates, email indicators, and behavioral artifacts with full normalization, deduplication, alias management, and canonical linking.
🧭 Every indicator structured. Every signal traceable. 🧭
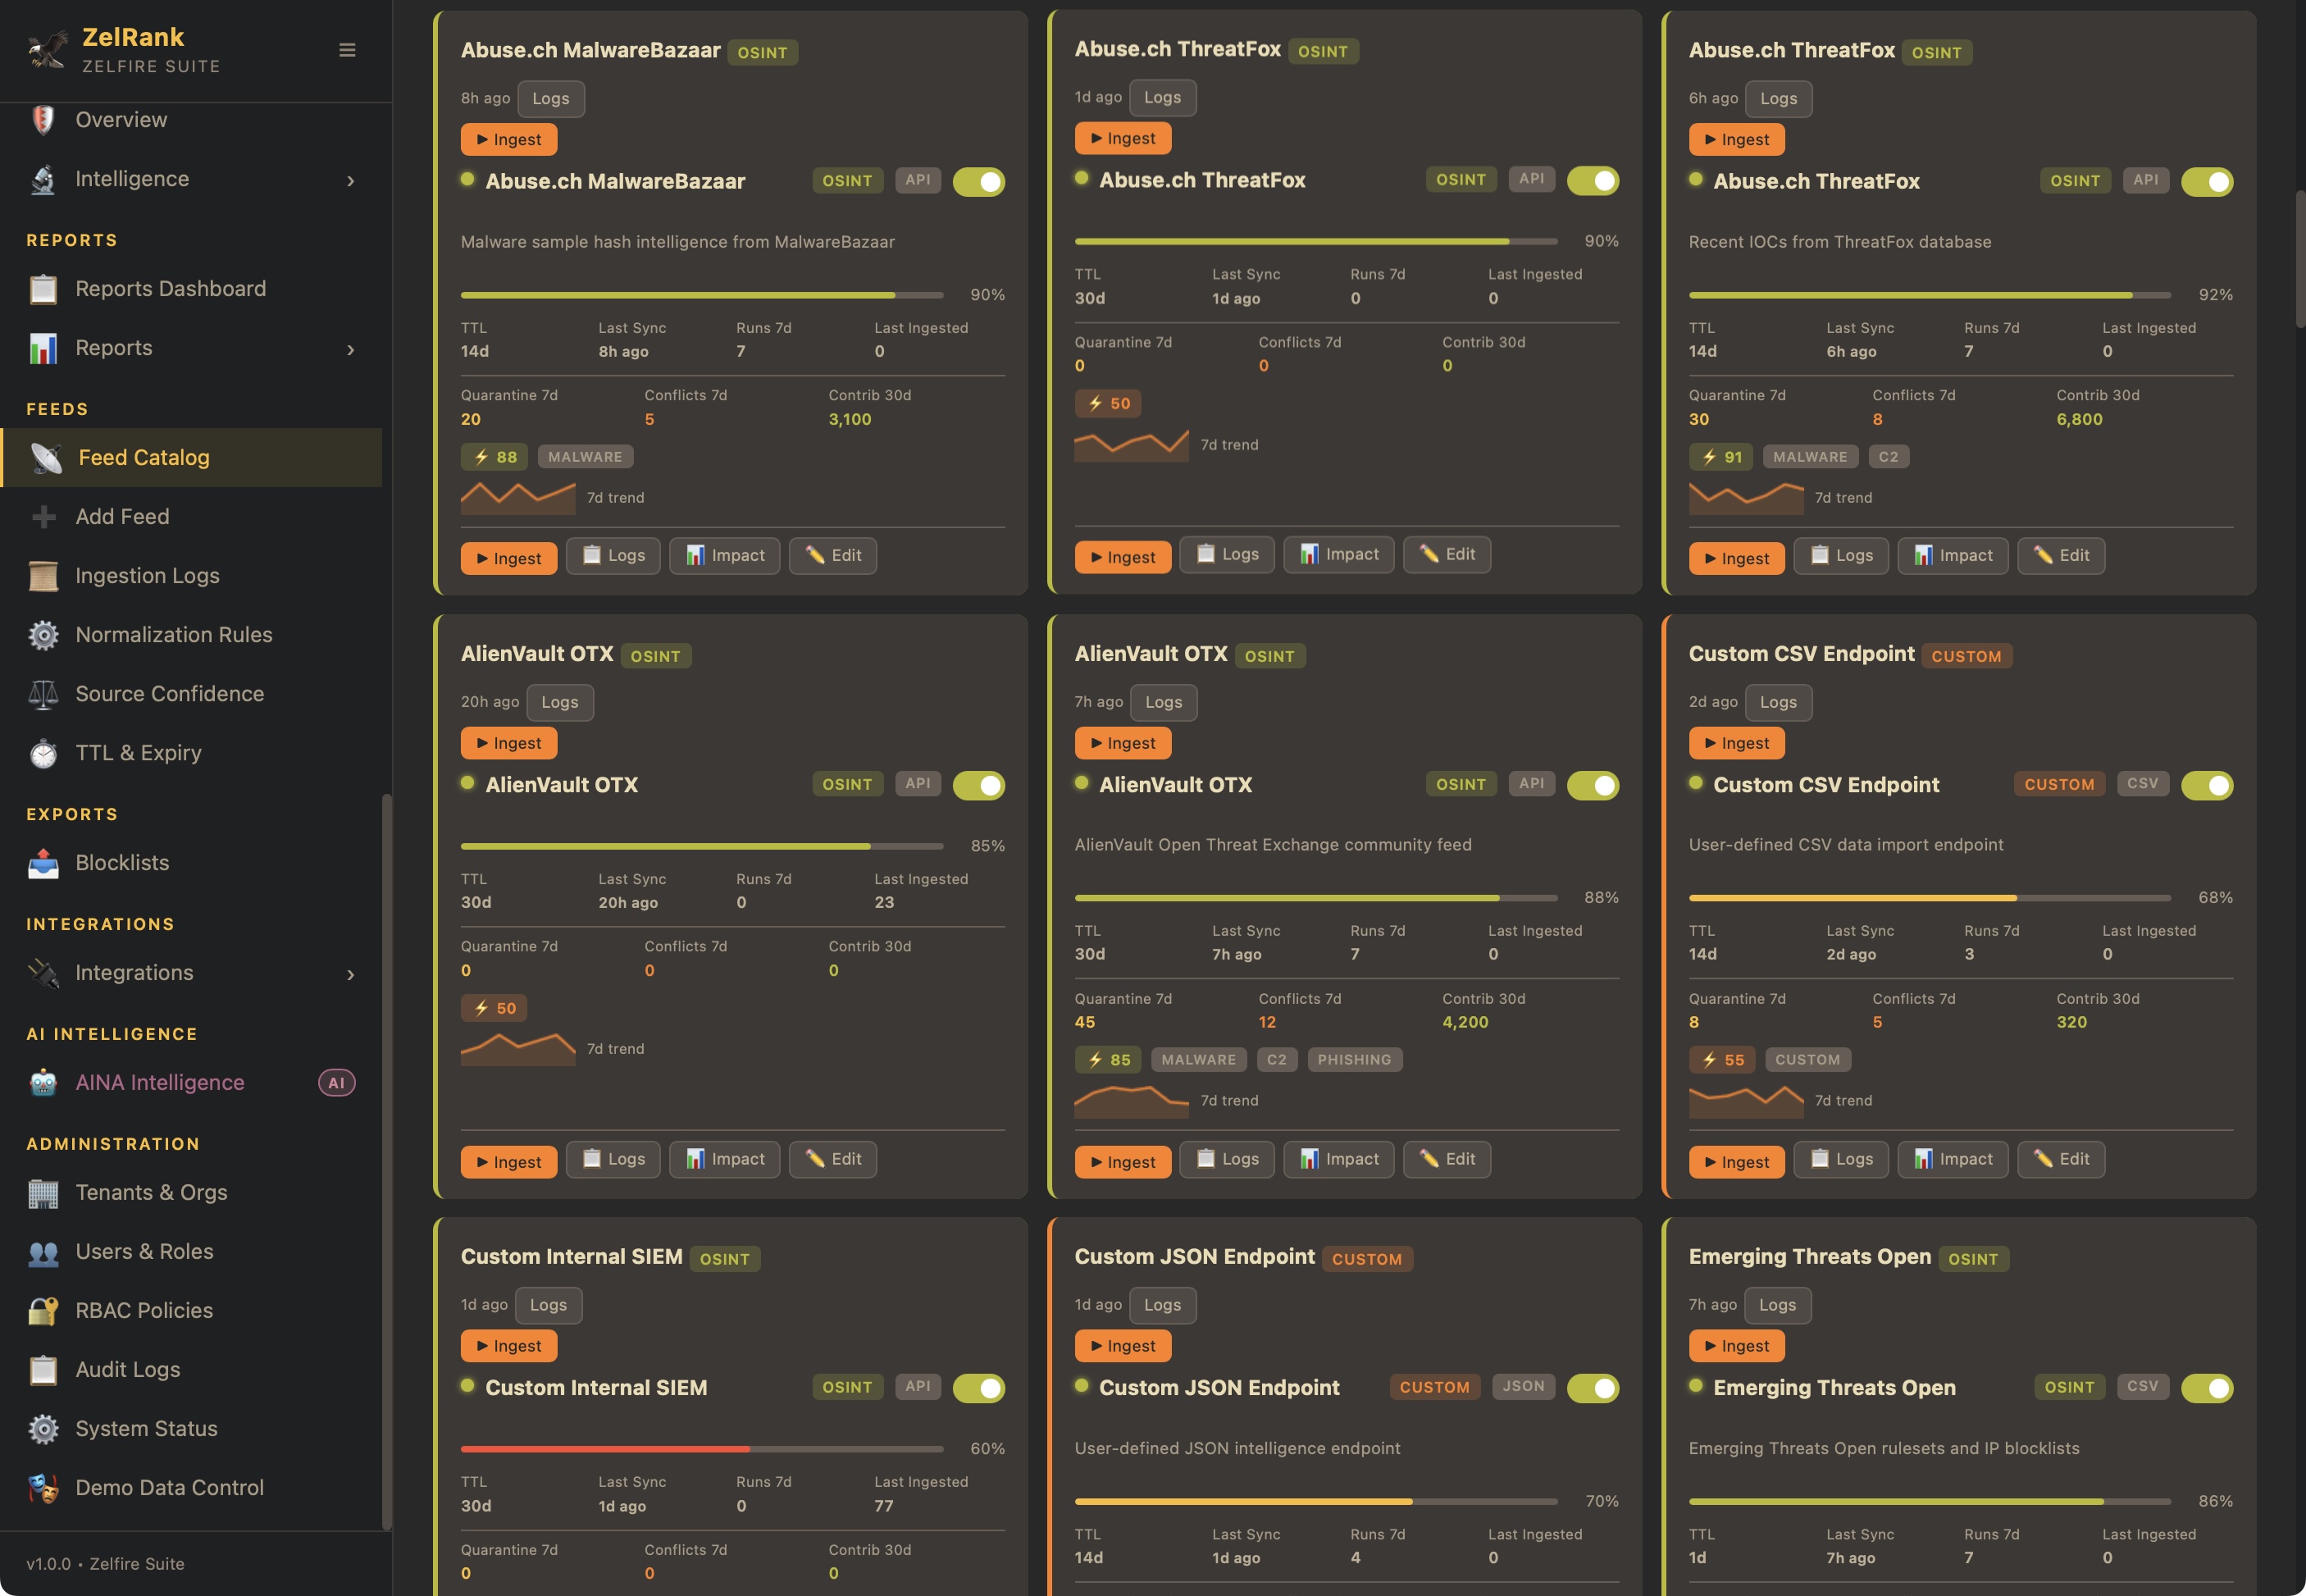
Ingests API, JSON, CSV, STIX, TAXII, and internal feeds with full observability, conflict handling, quarantine controls, and influence scoring.
🔗 Feeds are not chaos — they are supply chains. 🔗
Each feed is weighted based on reliability, conflict rate, and contribution, ensuring transparent intelligence prioritization.
📏 Trust is measured, not assumed. 📏
Complete run logs, error tracing, processing breakdown, retry control, and quarantine review dashboards.
🛰️ Every ingestion visible. Every anomaly traceable. 🛰️
ZelRank breaks down confidence and risk into feed weight, sightings impact, time decay, conflict penalties, and AI adjustments.
🔍 Explainable intelligence builds trust. 🔍
Correlates detections across ZelXDR, ZelScan, ZelWall, ZelMap, ZelCloud, and external feeds to increase accuracy.
🧩 Correlation creates certainty. 🧩
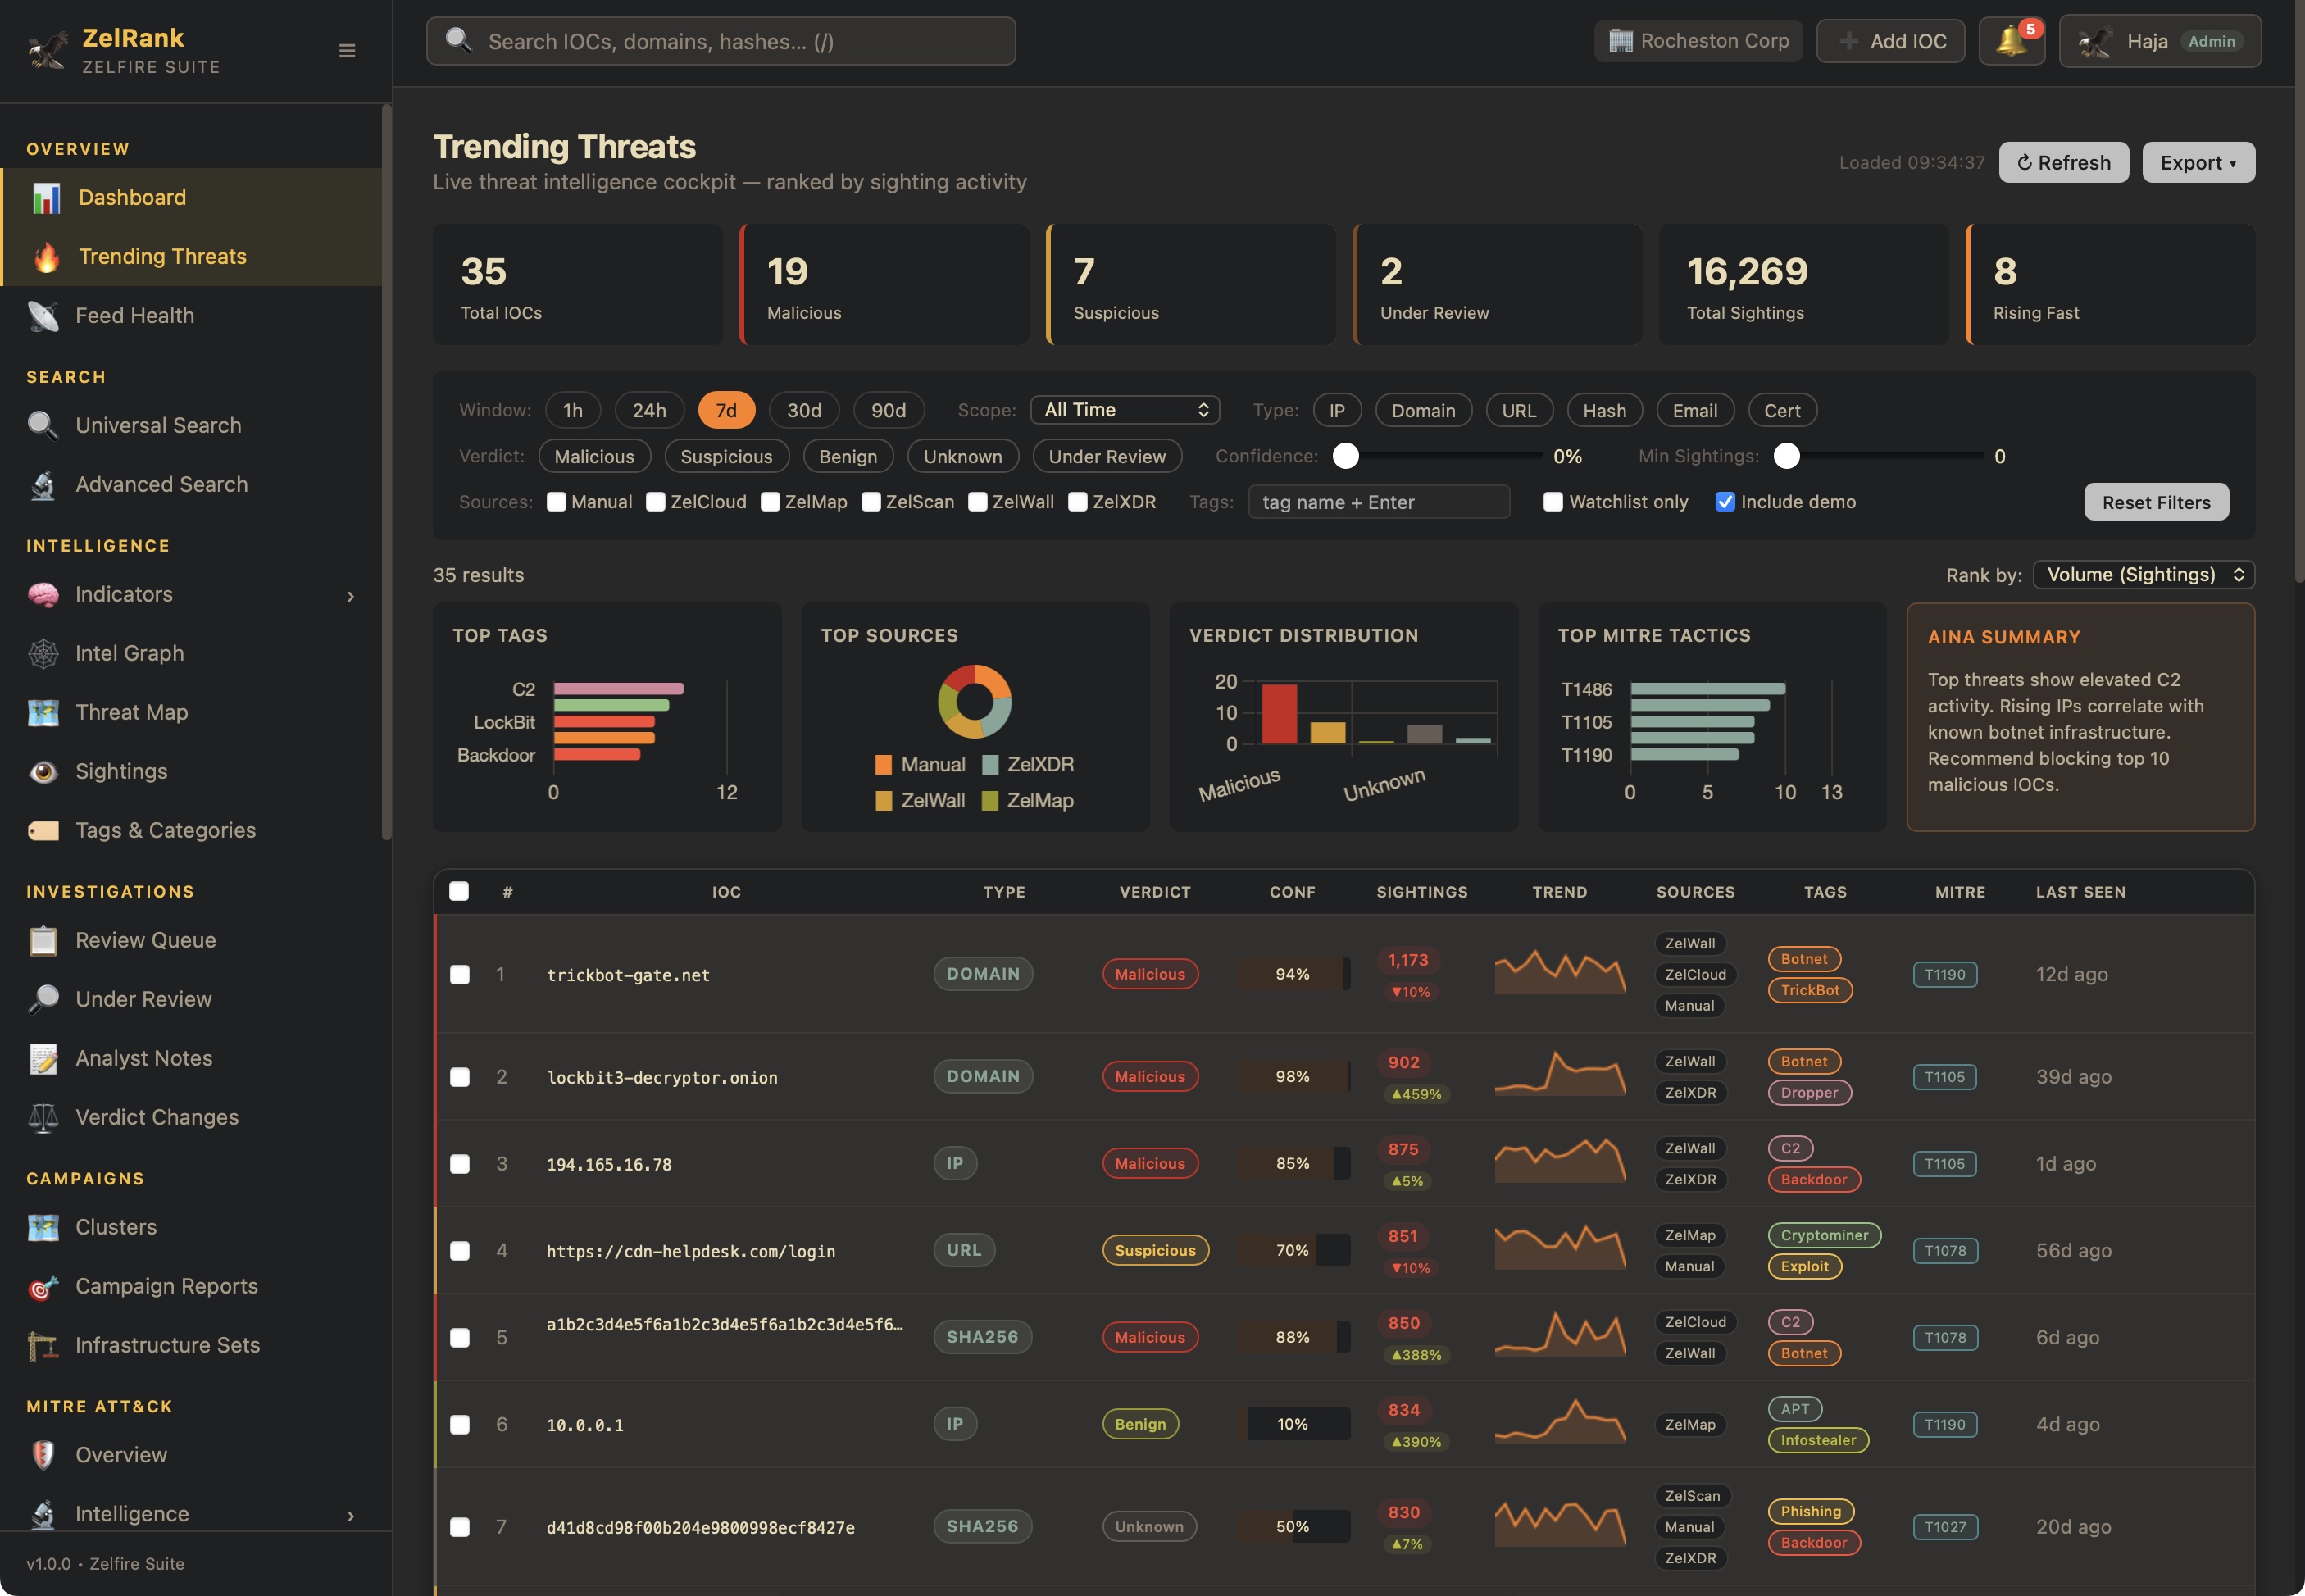
Velocity detection, spike analysis, source breakdown, and multi-product validation analytics.
📈 Patterns reveal intent. 📈
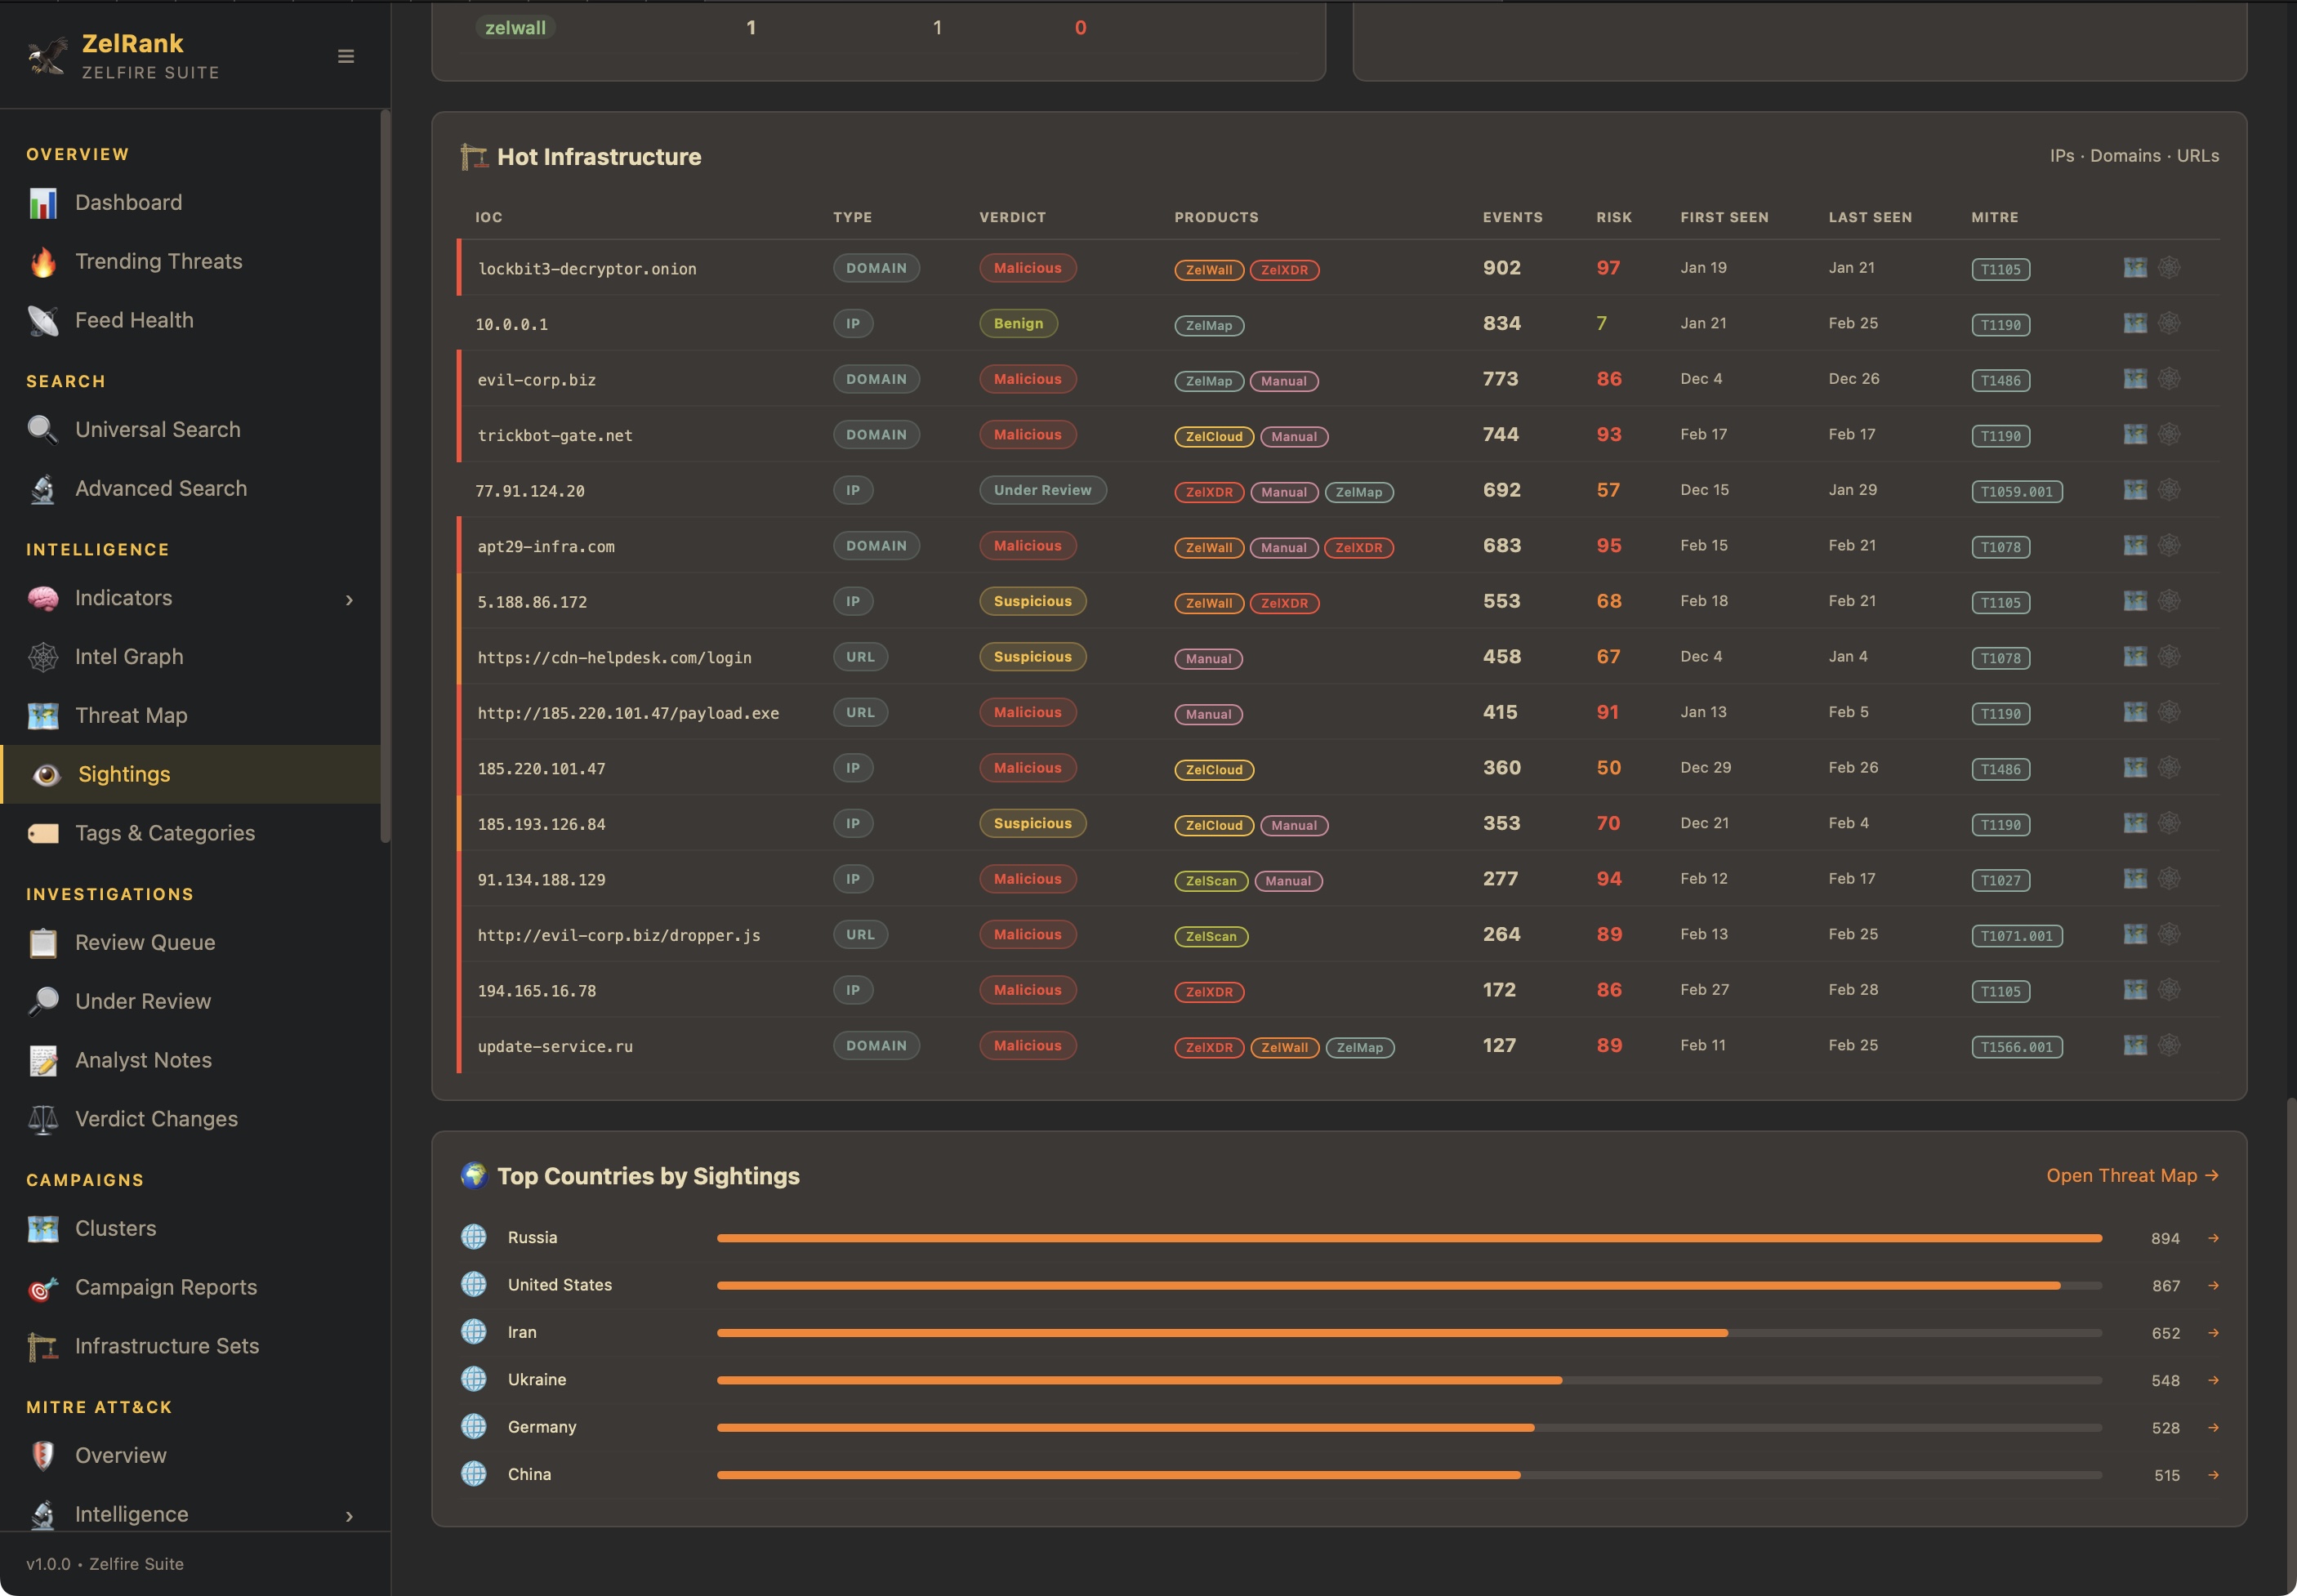
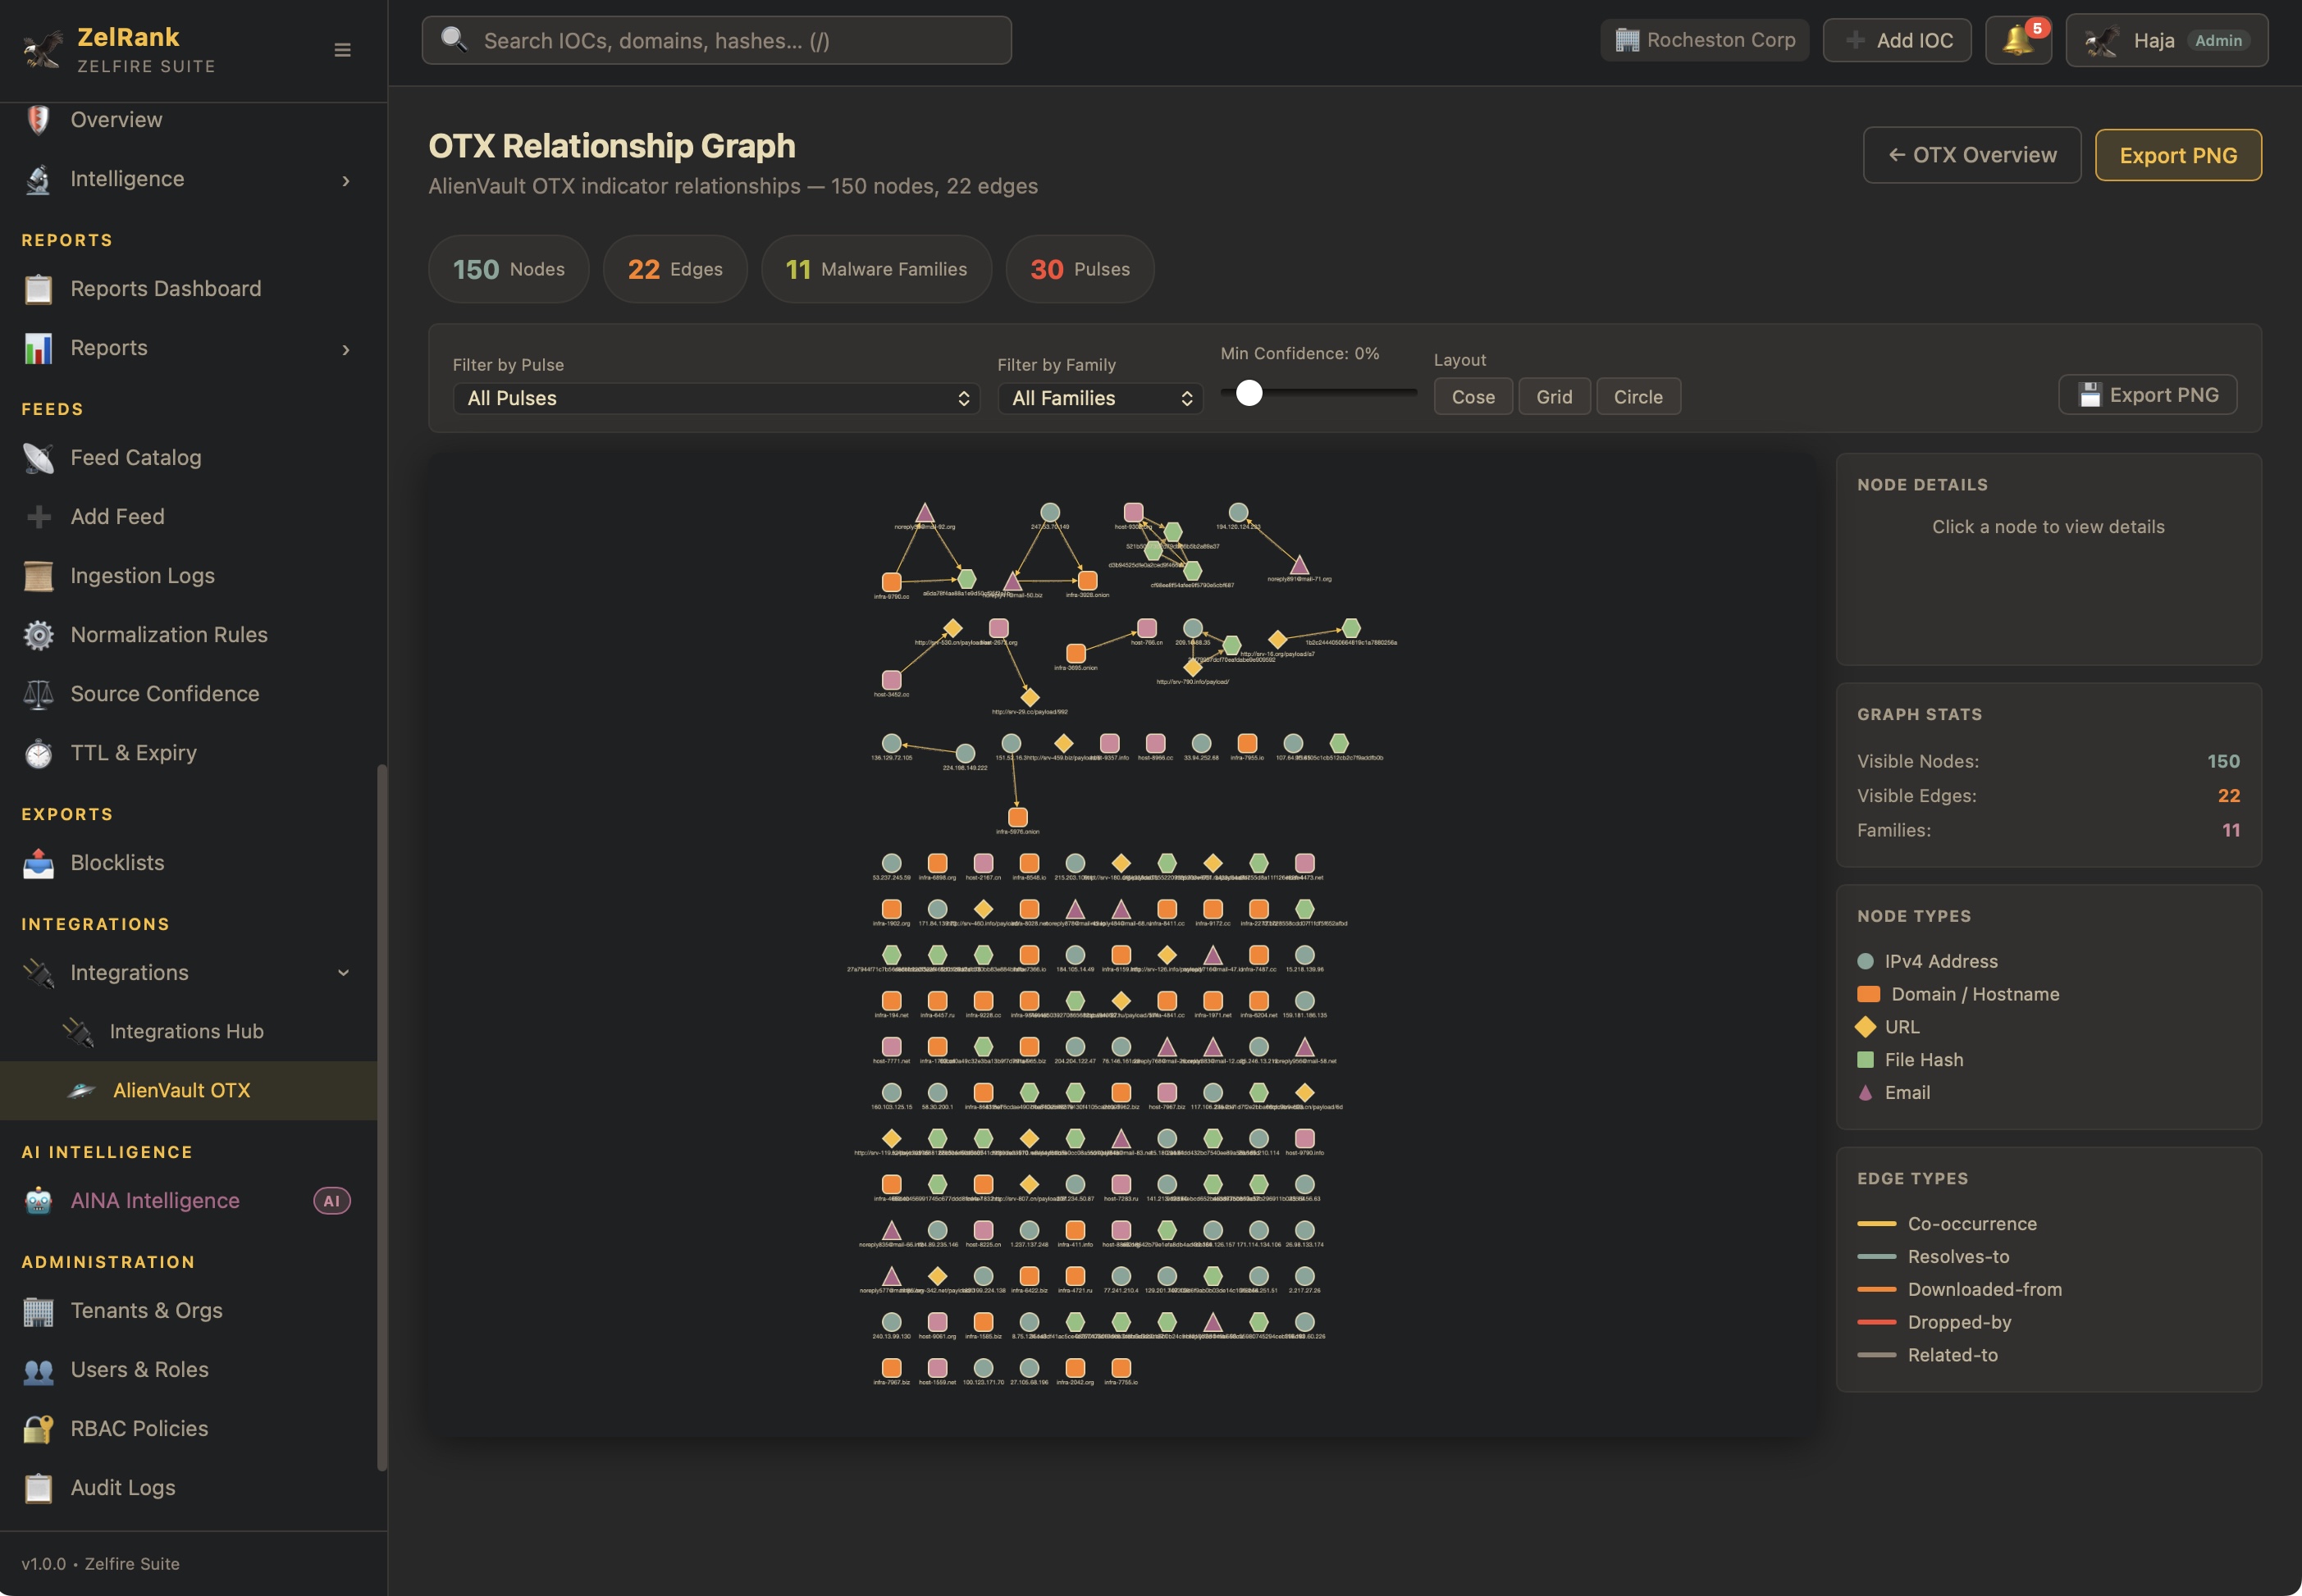
Dynamic graph visualization of IOC relationships, clustering, pathfinding, and infrastructure mapping.
🕸️ Threats are networks. So is your defense. 🕸️
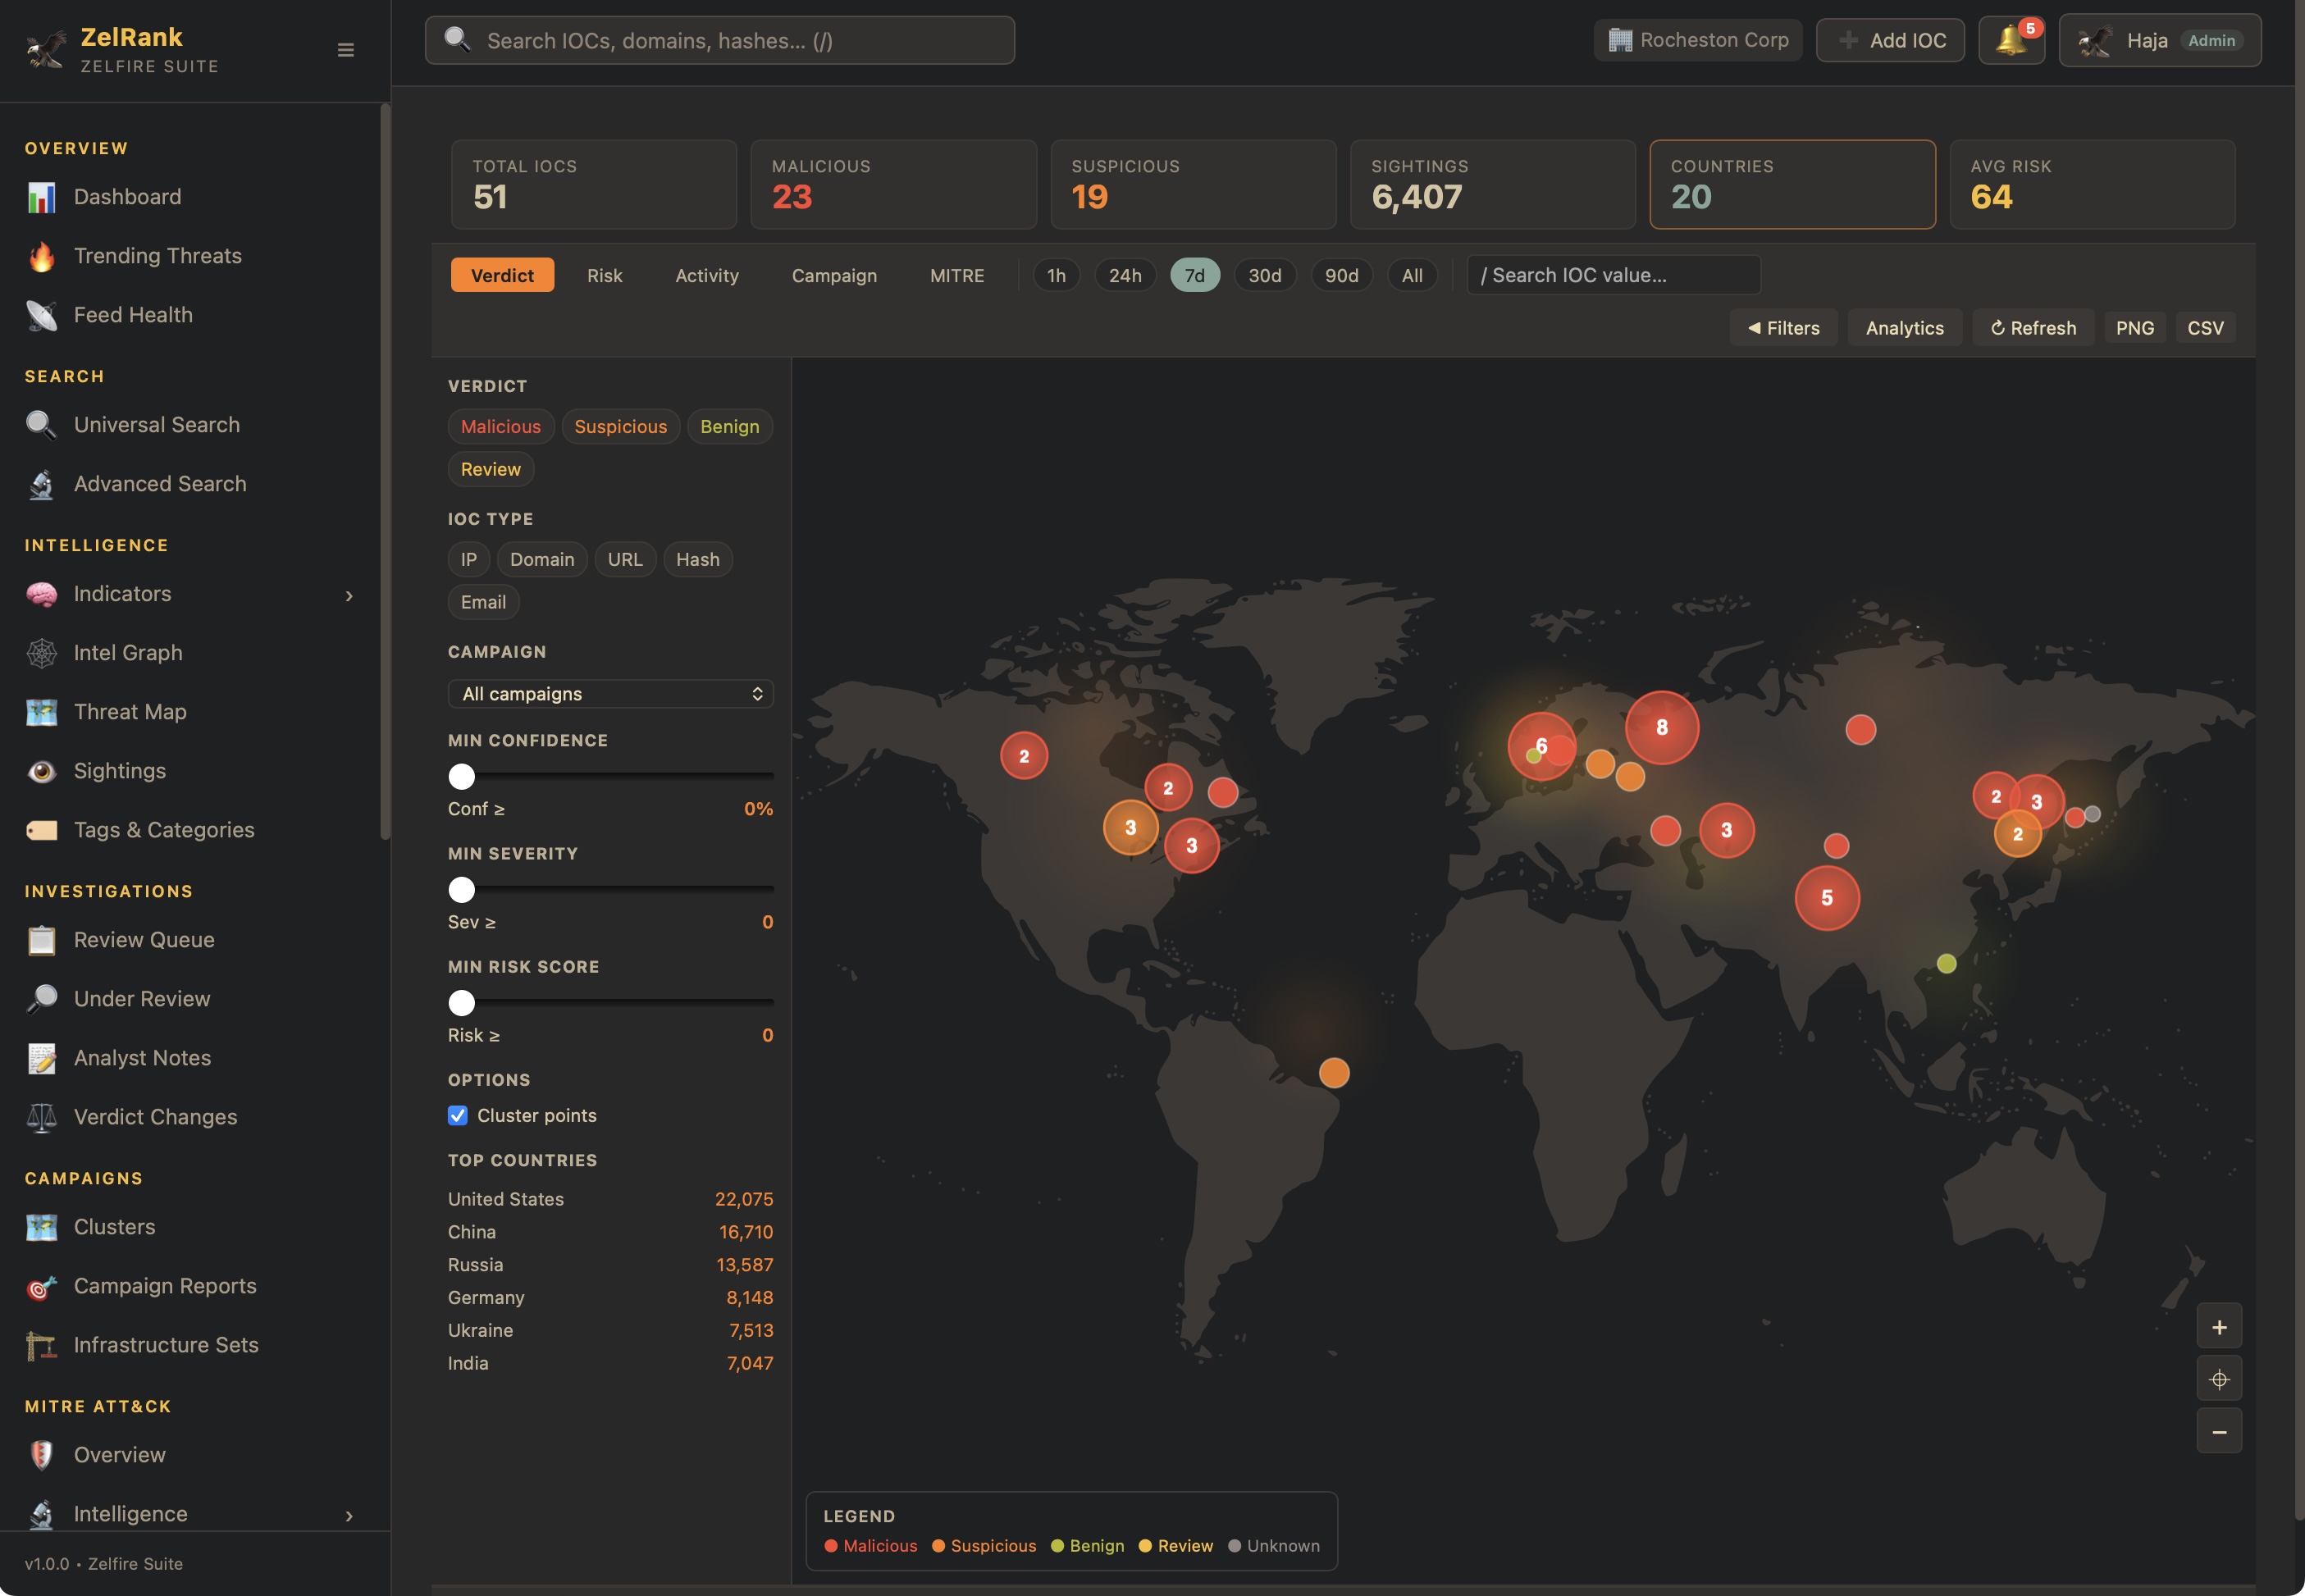
Interactive vector world map with heatmaps, clustering, geo filtering, and time-based playback.
🌍 See the threat landscape globally. 🌍
Track, analyze, and manage campaign lifecycles with attribution, MITRE mapping, and geo spread analysis.
📚 Campaigns are stories. ZelRank tells them. 📚
Automatic grouping of related infrastructure using density modeling and AI-assisted pattern detection.
🧬 From fragments to formation. 🧬
Identify high-density malicious infrastructure, shared nodes, multi-product confirmations, and dormant assets.
🏗️ Understand attacker infrastructure at scale. 🏗️
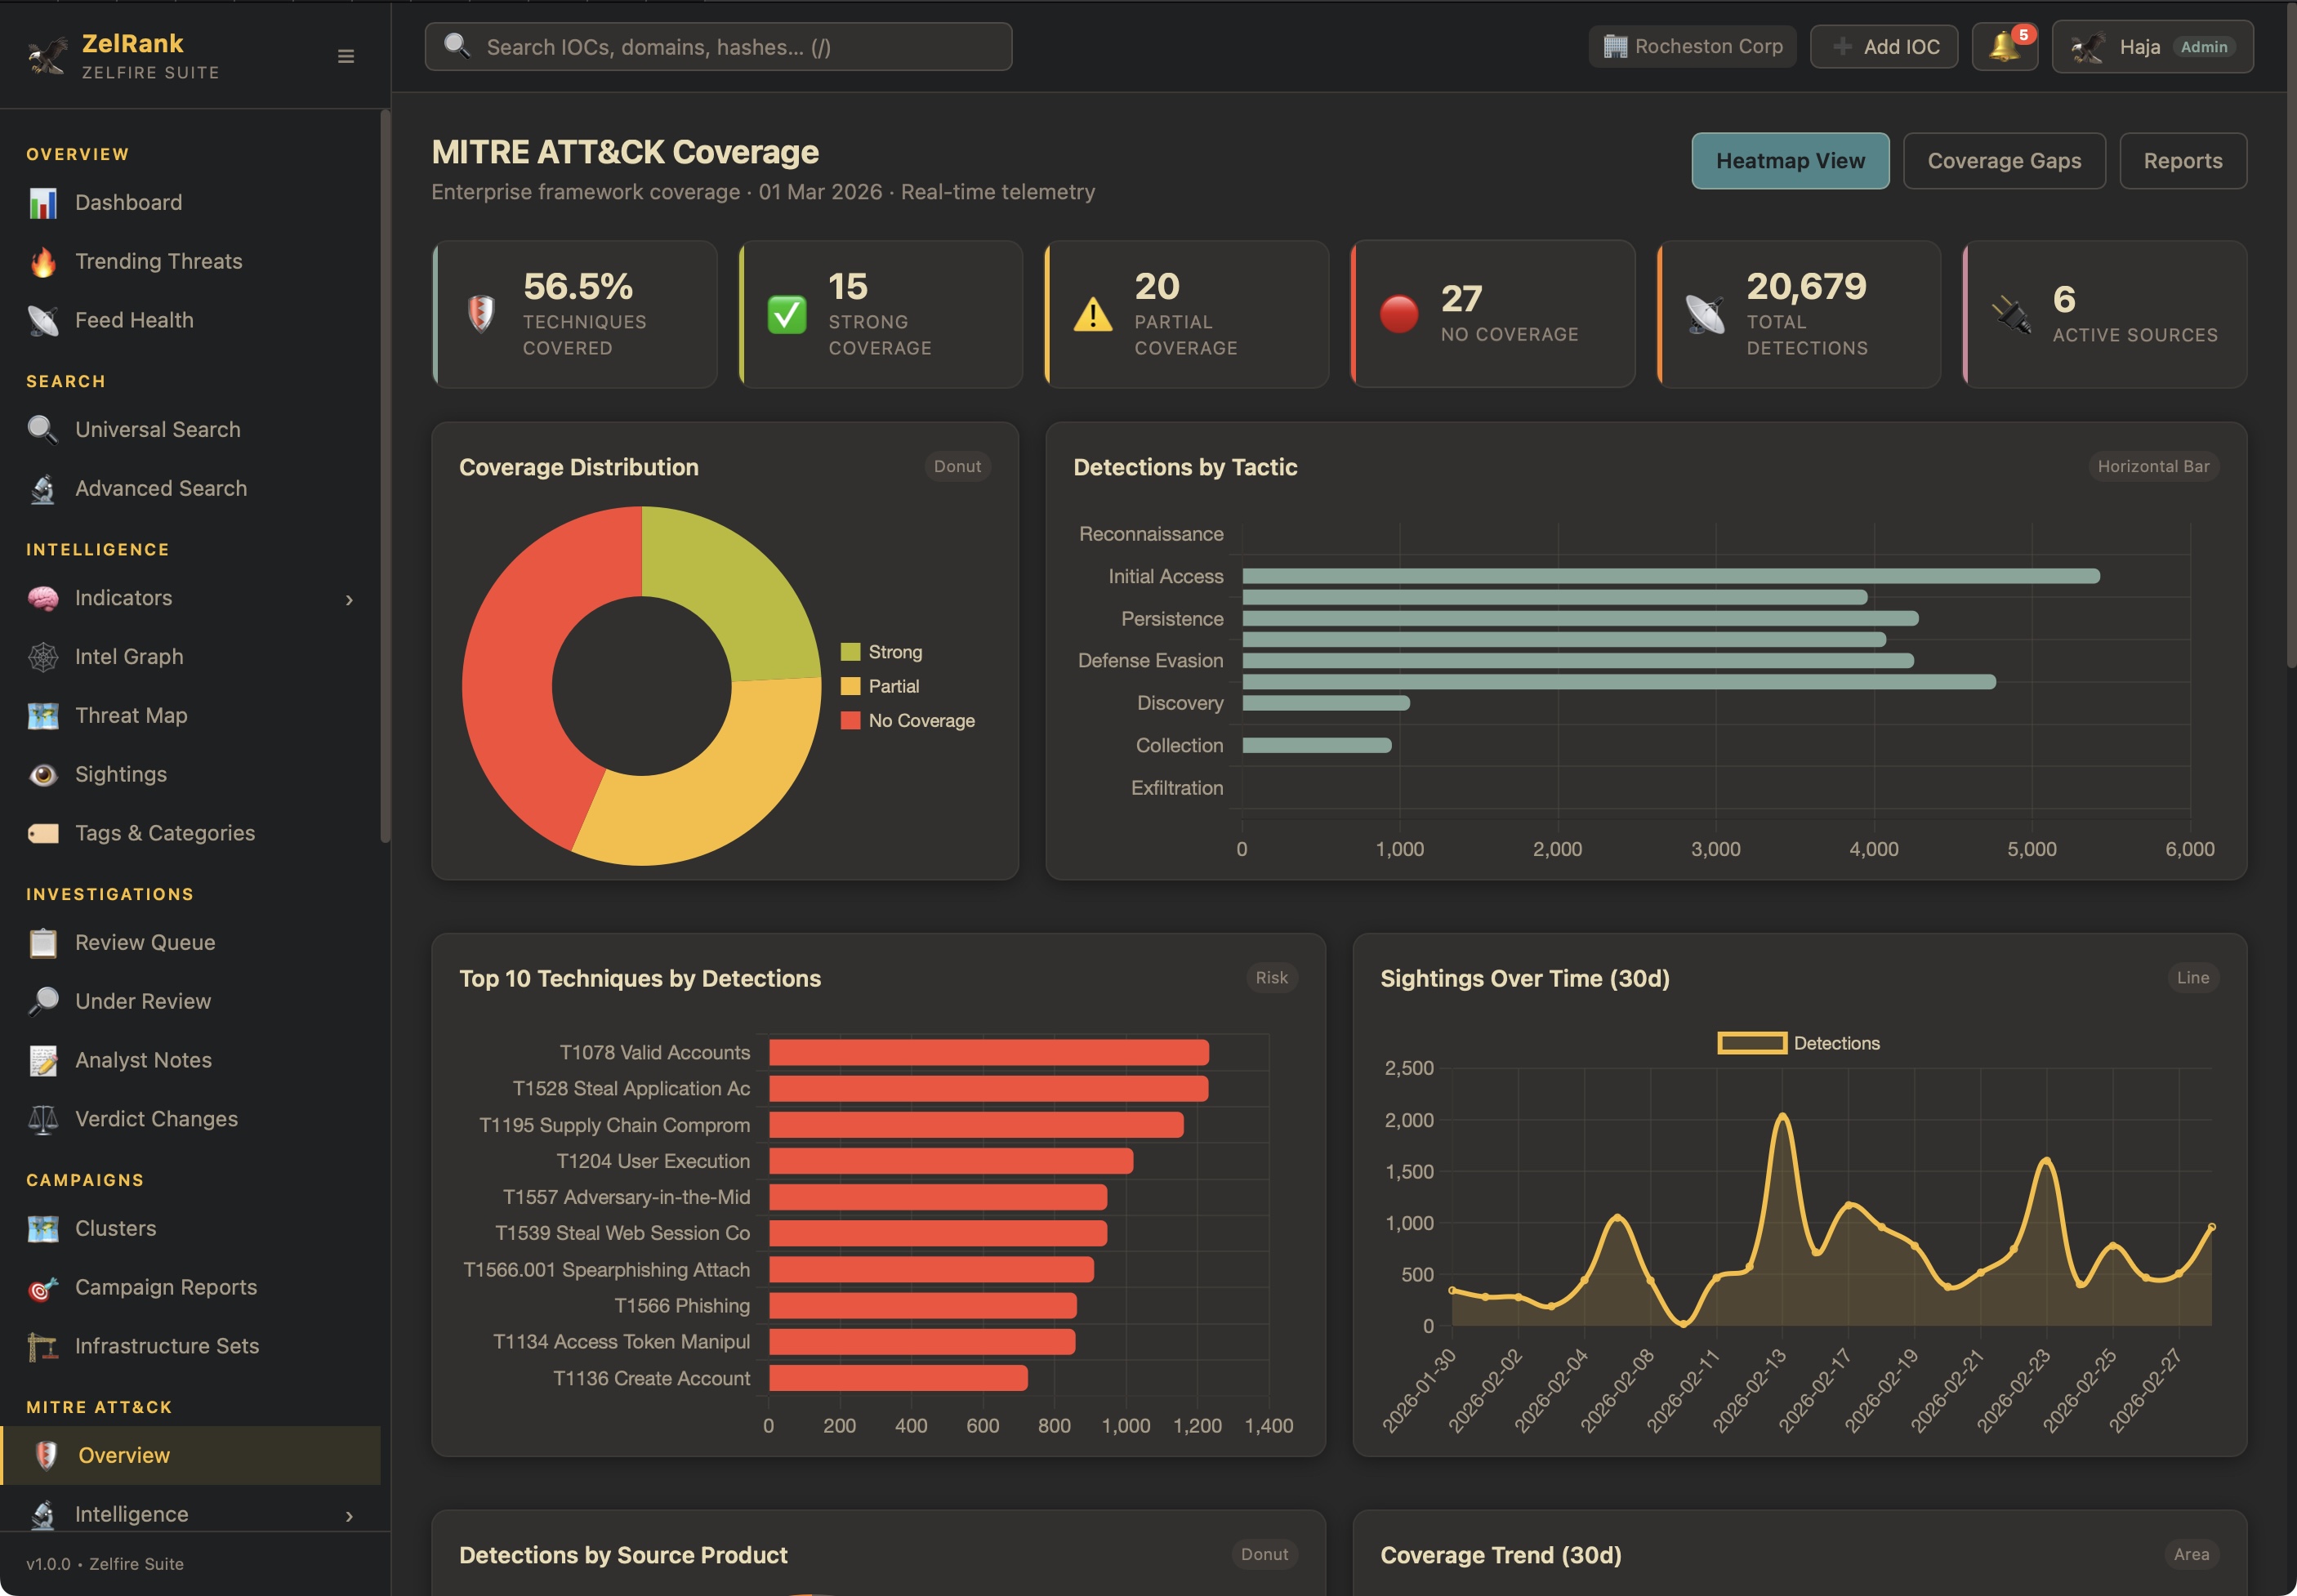
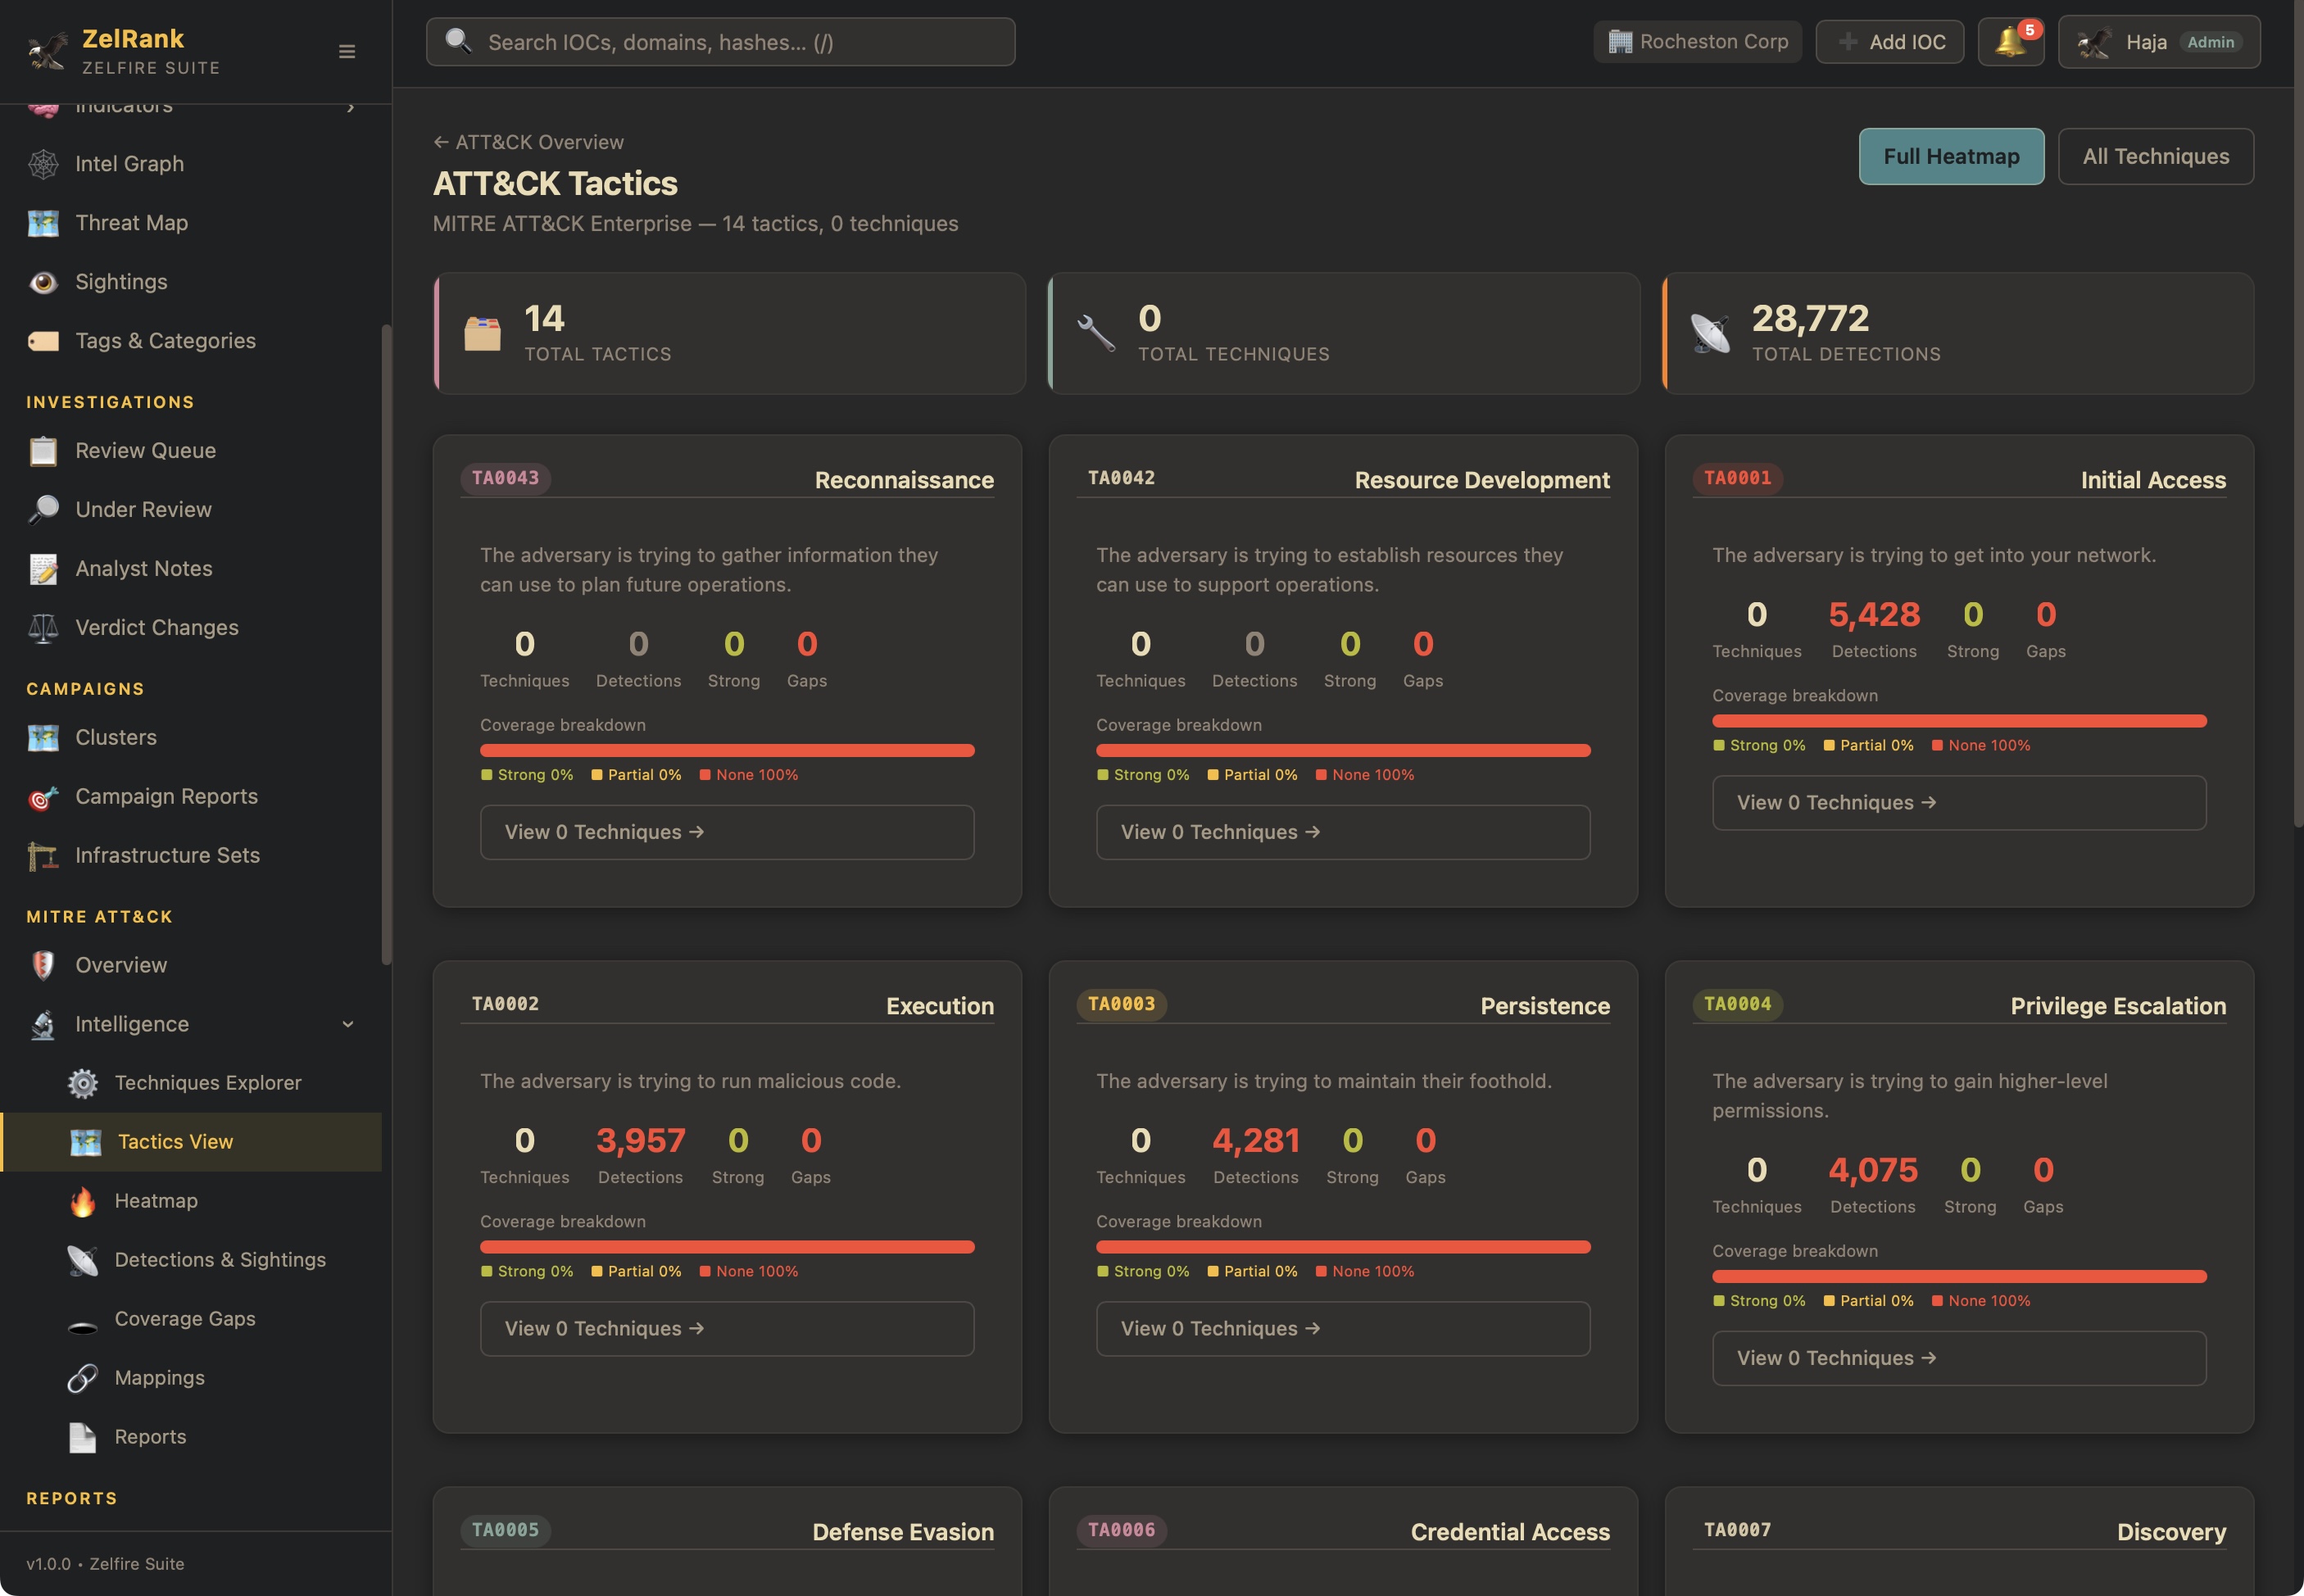
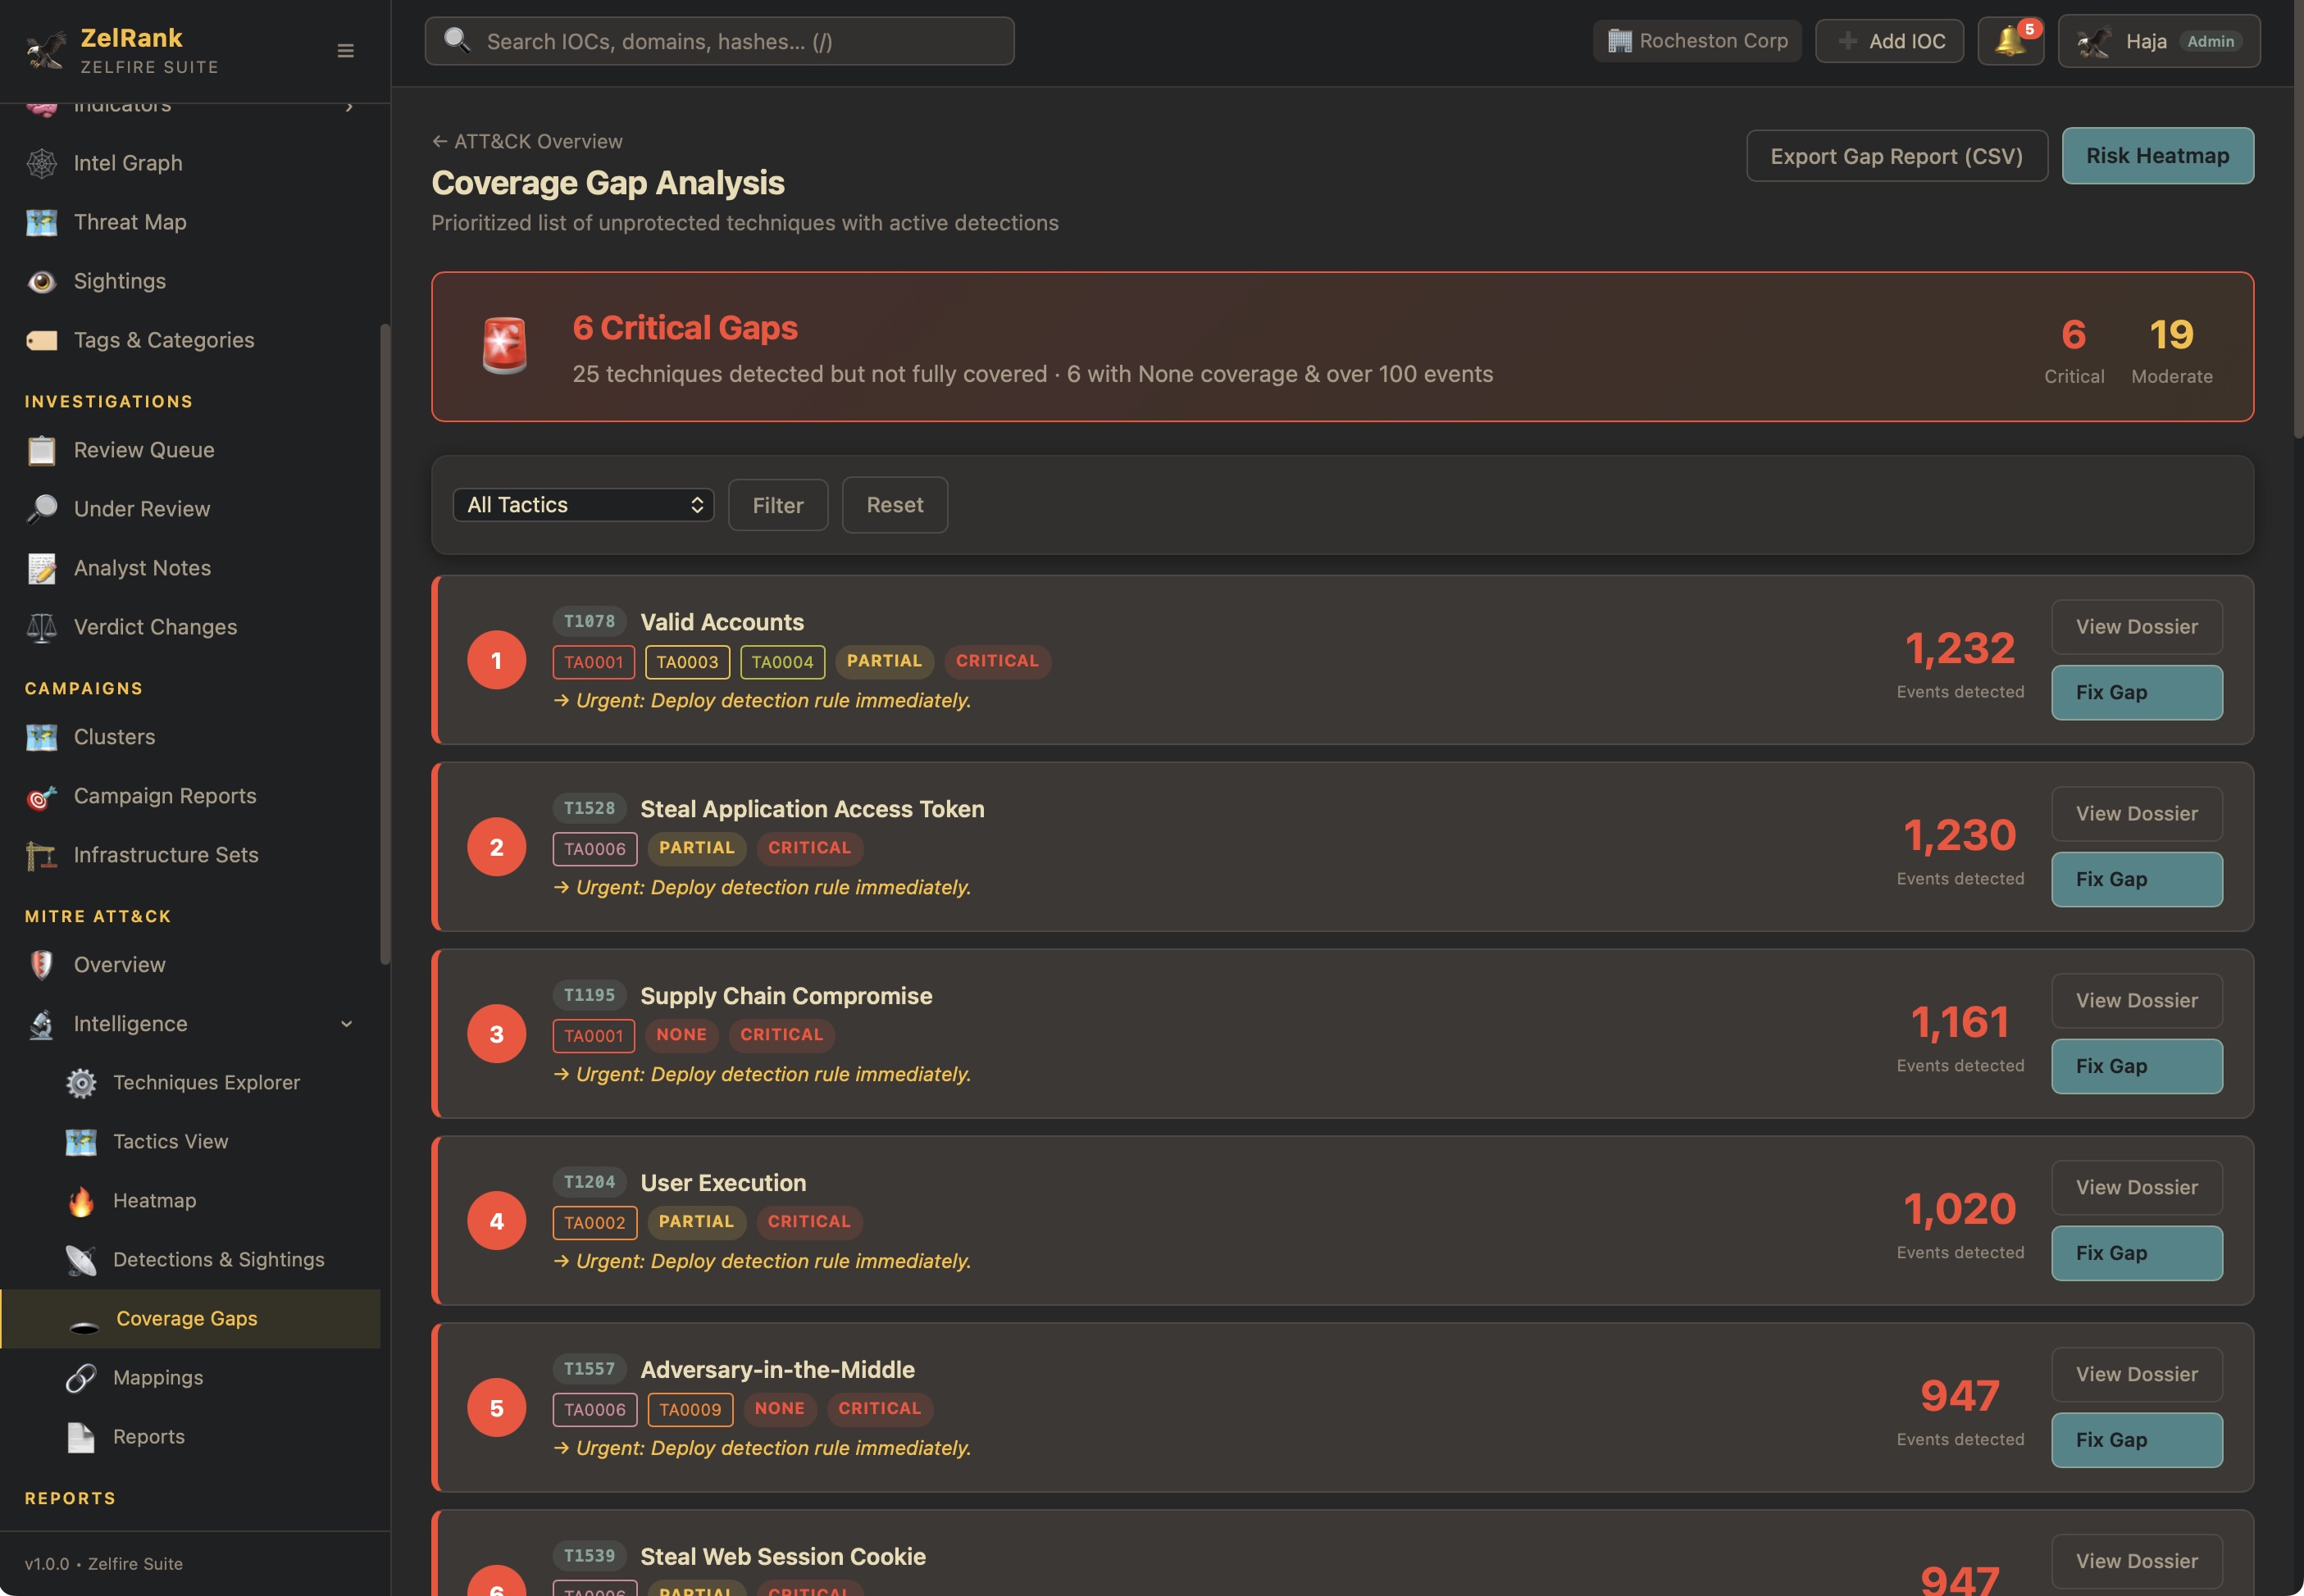
Full tactic and technique mapping, heatmaps, coverage analysis, and investigation-level alignment.
🎯 Strategic mapping meets tactical detection. 🎯
Dedicated intelligence workspace combining IOCs, timeline, evidence, graph view, and AI-assisted summaries.
🗂️ Investigations deserve structure. 🗂️
AI-powered threat briefs, IOC explanation, campaign narratives, anomaly detection, and predictive risk forecasting.
🤖 AI that understands intelligence. 🤖
Generates executive and technical intelligence briefs with actionable recommendations.
⚡ From data to direction in seconds. ⚡
Identifies rapid changes in threat activity and highlights high-risk emerging indicators.
🚨 Speed reveals escalation. 🚨
Granular expiration policies per IOC type and per feed to prevent stale intelligence pollution.
⏱️ Fresh intelligence is accurate intelligence. ⏱️
Automatically detects and resolves feed verdict conflicts with transparent override controls.
🧮 Disagreement is analyzed, not ignored. 🧮
Supports 40+ integrations including OTX, MISP, ThreatFox, MalwareBazaar, GreyNoise, and internal suite feeds.
🌐 An ecosystem, not a connector list. 🌐
Maps indicators to geographic distribution with region-level reporting and hotspot analysis.
🗺️ Threats move. We track their path. 🗺️
AI-assisted predictions for infrastructure expansion, campaign escalation, and regional spread.
🔮 Intelligence should look forward. 🔮
Feed overlap matrices identify redundancy and highlight unique intelligence contributors.
🧪 Know what is unique. Remove what is redundant. 🧪
Executive-ready reports with customizable branding, cover pages, confidentiality labels, and export formats.
📝 Intelligence ready for the boardroom. 📝
Every action logged — ingestion, verdict changes, TTL updates, AI suggestions, investigations.
🧾 Transparency builds credibility. 🧾
User-isolated intelligence environments with strict data separation and role-based access control.
🔐 Secure by architecture. 🔐
Interactive breakdown of how each indicator’s risk score is calculated.
🧯 See how intelligence is formed. 🧯
Native integration with ZelXDR, ZelScan, ZelMap, ZelWall, ZelCloud, and ZelSOAR.
🧠 Intelligence integrated across defense layers. 🧠
Exclusively licensed to RCCE students, ZelRank trains the next generation of cybersecurity engineers on real-world intelligence systems.
🏆 Master intelligence. Lead defense. 🏆
CTI platforms are notoriously difficult to configure and integrate. ZelRank eliminates that complexity through structured ingestion, explainable scoring, and seamless integration.
🧭 Complexity engineered into clarity. 🧭
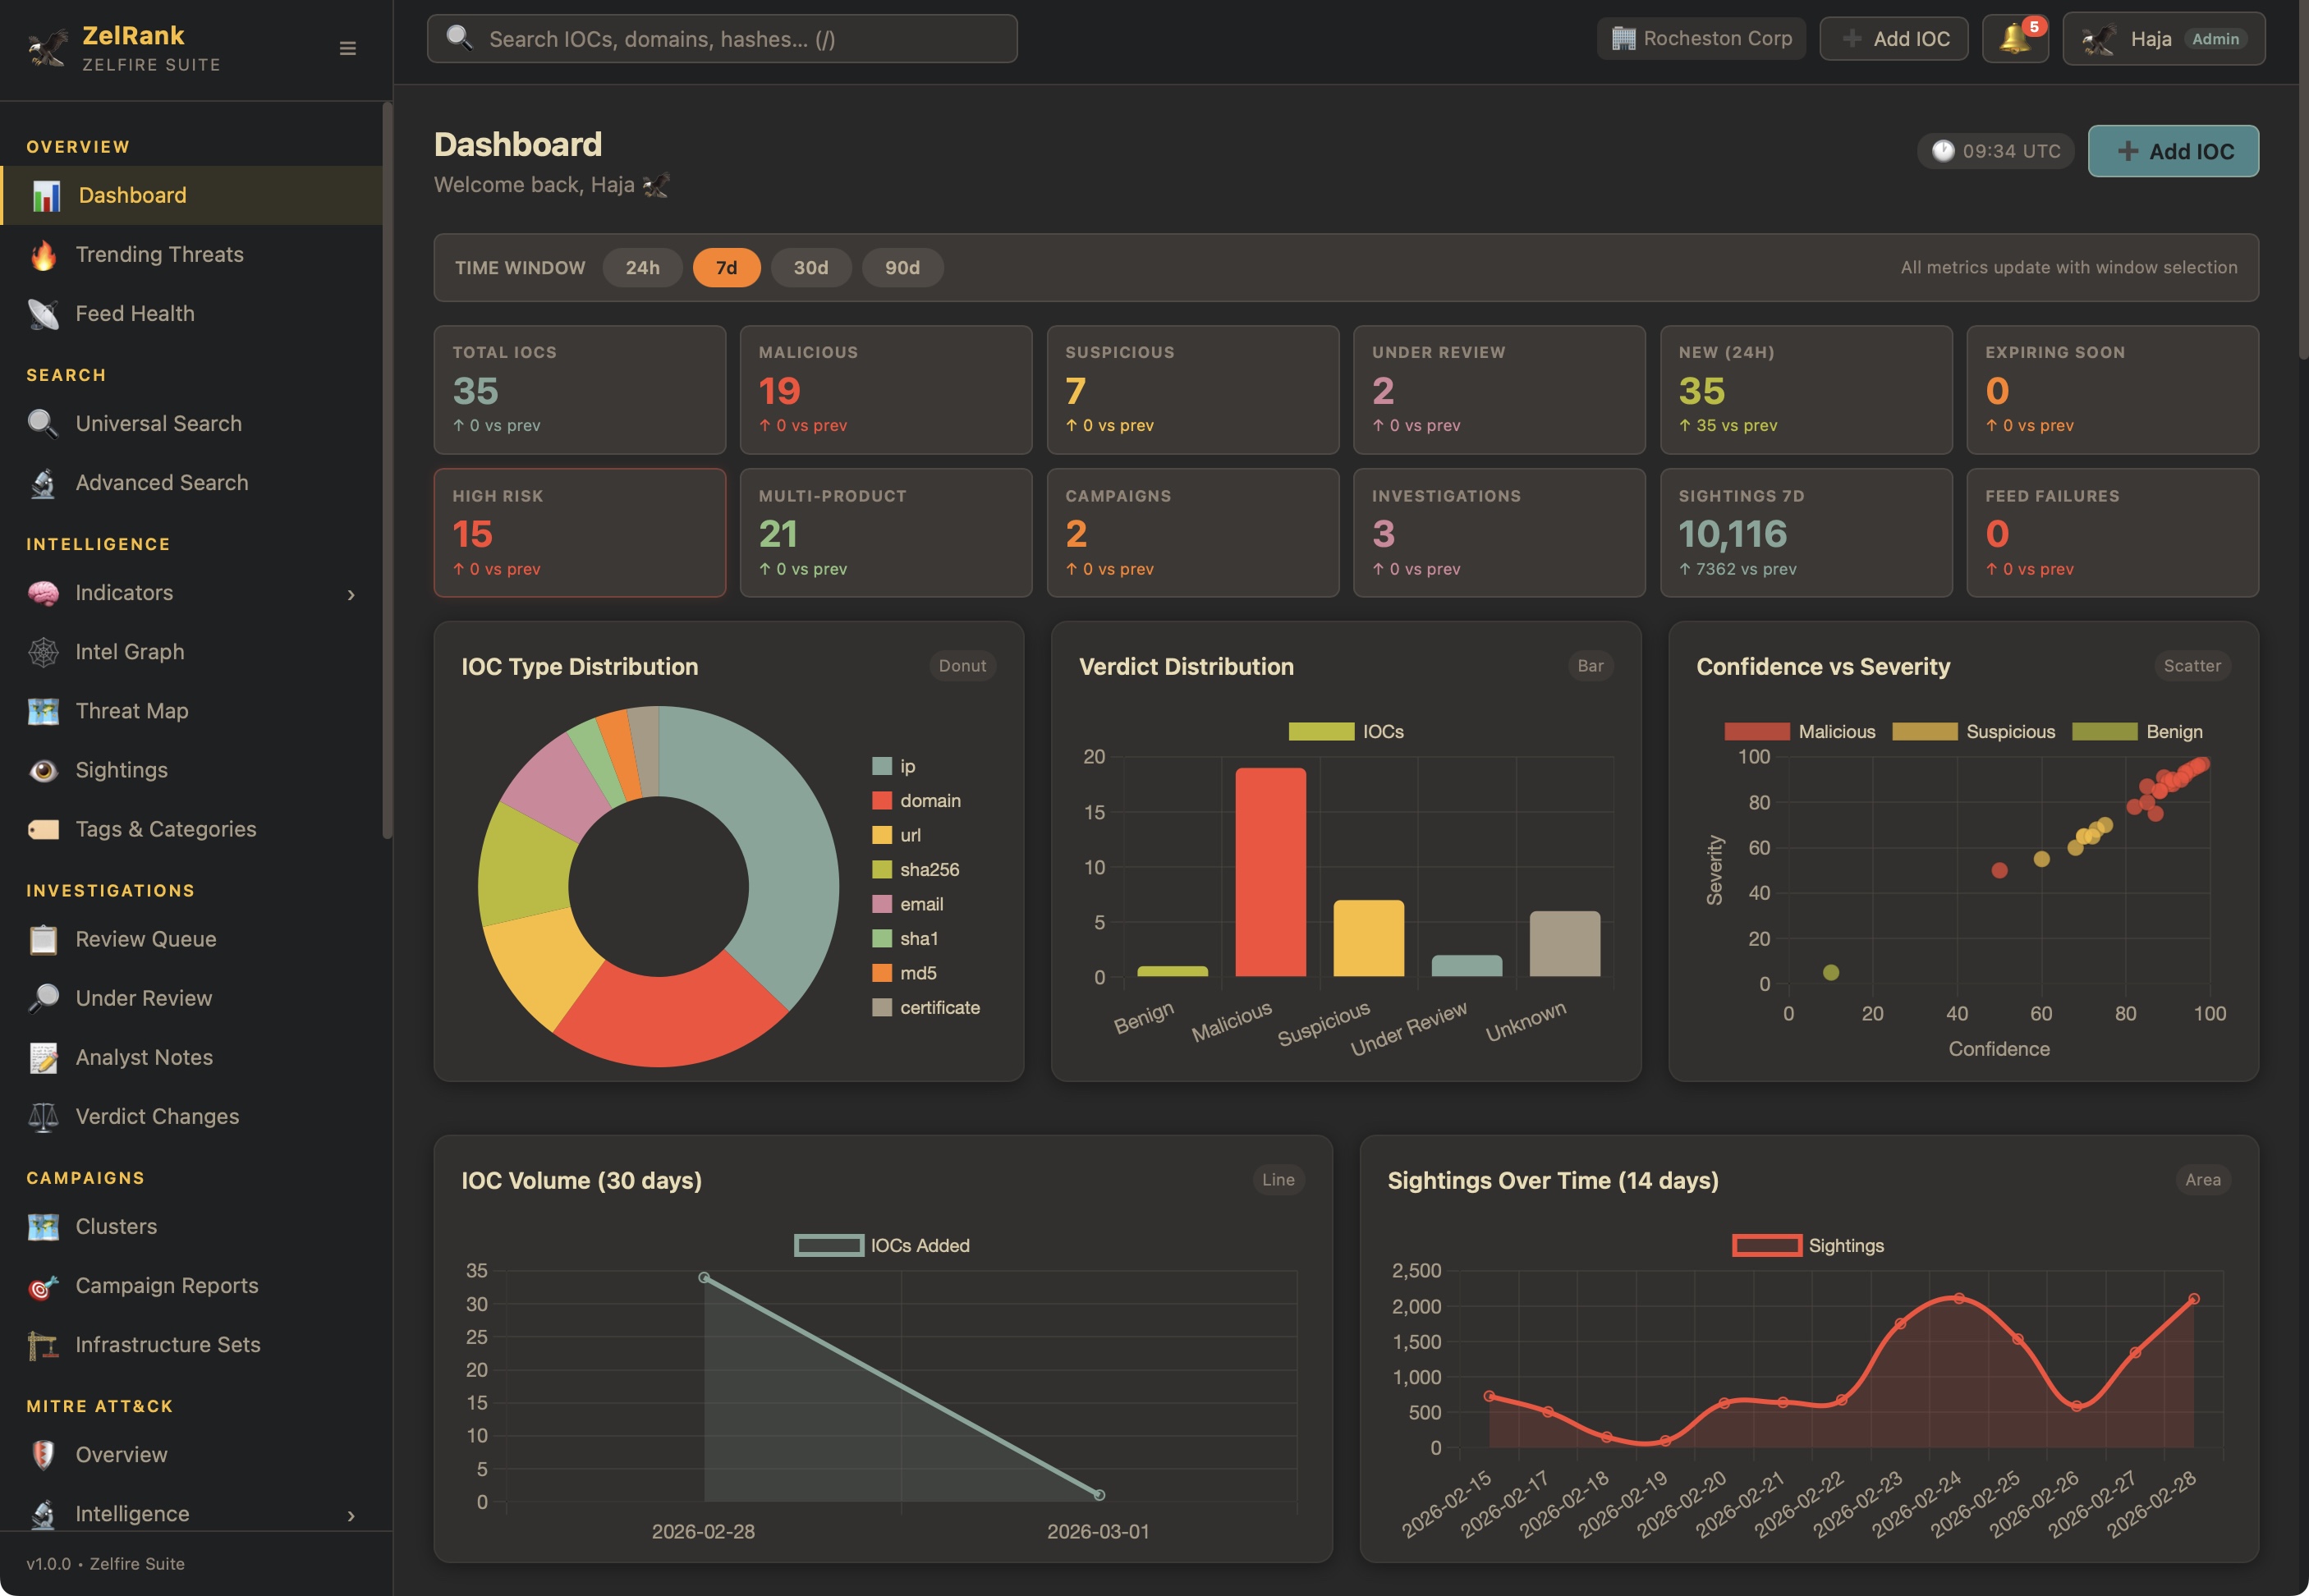
Dashboards, graphs, heatmaps, timelines, and analytics designed for operational and strategic teams alike.
🎛️ Intelligence you can see, measure, and act upon. 🎛️
ZelRank represents a shift from reactive intelligence collection to proactive, AI-enhanced, explainable cyber threat intelligence management.
🚀 The intelligence engine of tomorrow. 🚀
ZelRank leverages ZelC to orchestrate intelligence workflows, manage autonomous AI agents, automate feed logic, and control scoring behaviors. Program enrichment pipelines, correlation rules, MITRE mappings, and investigation automation directly inside the engine.
🧠 ZelC gives intelligence the power of code. 🧠
ZelRank integrates natively with ZelXDR, ZelScan, ZelMap, ZelWall, ZelCloud, ZelSOAR, AINA, Reporting, Threat Map, Intel Graph, and Investigation Workspace for a synchronized, closed-loop intelligence ecosystem.
🌊 Intelligence that flows across every layer of defense. 🌊
Rocheston ZelRank is exclusively licensed to RCCE students and embedded in the curriculum as the primary CTI platform, enabling hands‑on experience with ingestion pipelines, scoring models, campaigns, clusters, infrastructure sets, graph and geo intelligence, AINA AI, and ZelC automation.
🎓 Learn CTI the way it runs in the real world — only in RCCE. 🎓
UNDER THE HOOD
Architecture, integrations, security controls, and operational details for ZelRank.
ZelRank consolidates OSINT, premium feeds, internal telemetry, and AI-derived intelligence into a single platform for a unified intelligence layer.
Supports IPs, domains, URLs, hashes, certificates, email, and behavioral artifacts with normalization, deduplication, alias management, and canonical linking.
Ingests API, JSON, CSV, STIX, TAXII, and internal feeds with observability, conflict handling, quarantine controls, and influence scoring.
Weights feeds by reliability, conflict rate, and contribution to transparently prioritize intelligence.
Run logs, error tracing, processing breakdown, retry control, and quarantine review dashboards.
Breaks down confidence and risk into feed weight, sightings impact, time decay, conflict penalties, and AI adjustments.
Correlates detections across ZelXDR, ZelScan, ZelWall, ZelMap, ZelCloud, and external feeds to increase accuracy.
Includes velocity detection, spike analysis, source breakdown, and multi-product validation analytics.
Dynamic visualization of IOC relationships, clustering, pathfinding, and infrastructure mapping.
Interactive world map with heatmaps, clustering, geo filtering, and time-based playback.
Track and manage campaign lifecycles with attribution, MITRE mapping, and geo spread analysis.
Automatic grouping of related infrastructure using density modeling and AI-assisted pattern detection.
Identify high-density malicious infrastructure, shared nodes, multi-product confirmations, and dormant assets.
Full tactic and technique mapping, heatmaps, coverage analysis, and investigation-level alignment.
Dedicated workspace combining IOCs, timeline, evidence, graph view, and AI-assisted summaries.
AI-powered threat briefs, IOC explanation, campaign narratives, anomaly detection, and predictive risk forecasting.
Generates executive and technical intelligence briefs with actionable recommendations.
Identifies rapid changes in threat activity and highlights high‑risk emerging indicators.
Granular expiration policies per IOC type and per feed to prevent stale intelligence pollution.
Automatically detects and resolves feed verdict conflicts with transparent override controls.
Supports 40+ integrations including OTX, MISP, ThreatFox, MalwareBazaar, GreyNoise, and internal suite feeds.
Maps indicators to geographic distribution with region-level reporting and hotspot analysis.
AI-assisted predictions for infrastructure expansion, campaign escalation, and regional spread.
Overlap matrices identify redundancy and highlight unique intelligence contributors.
Executive-ready reports with customizable branding, confidentiality labels, and export formats.
Every action logged — ingestion, verdict changes, TTL updates, AI suggestions, and investigations.
User‑isolated intelligence environments with strict data separation and role‑based access control.
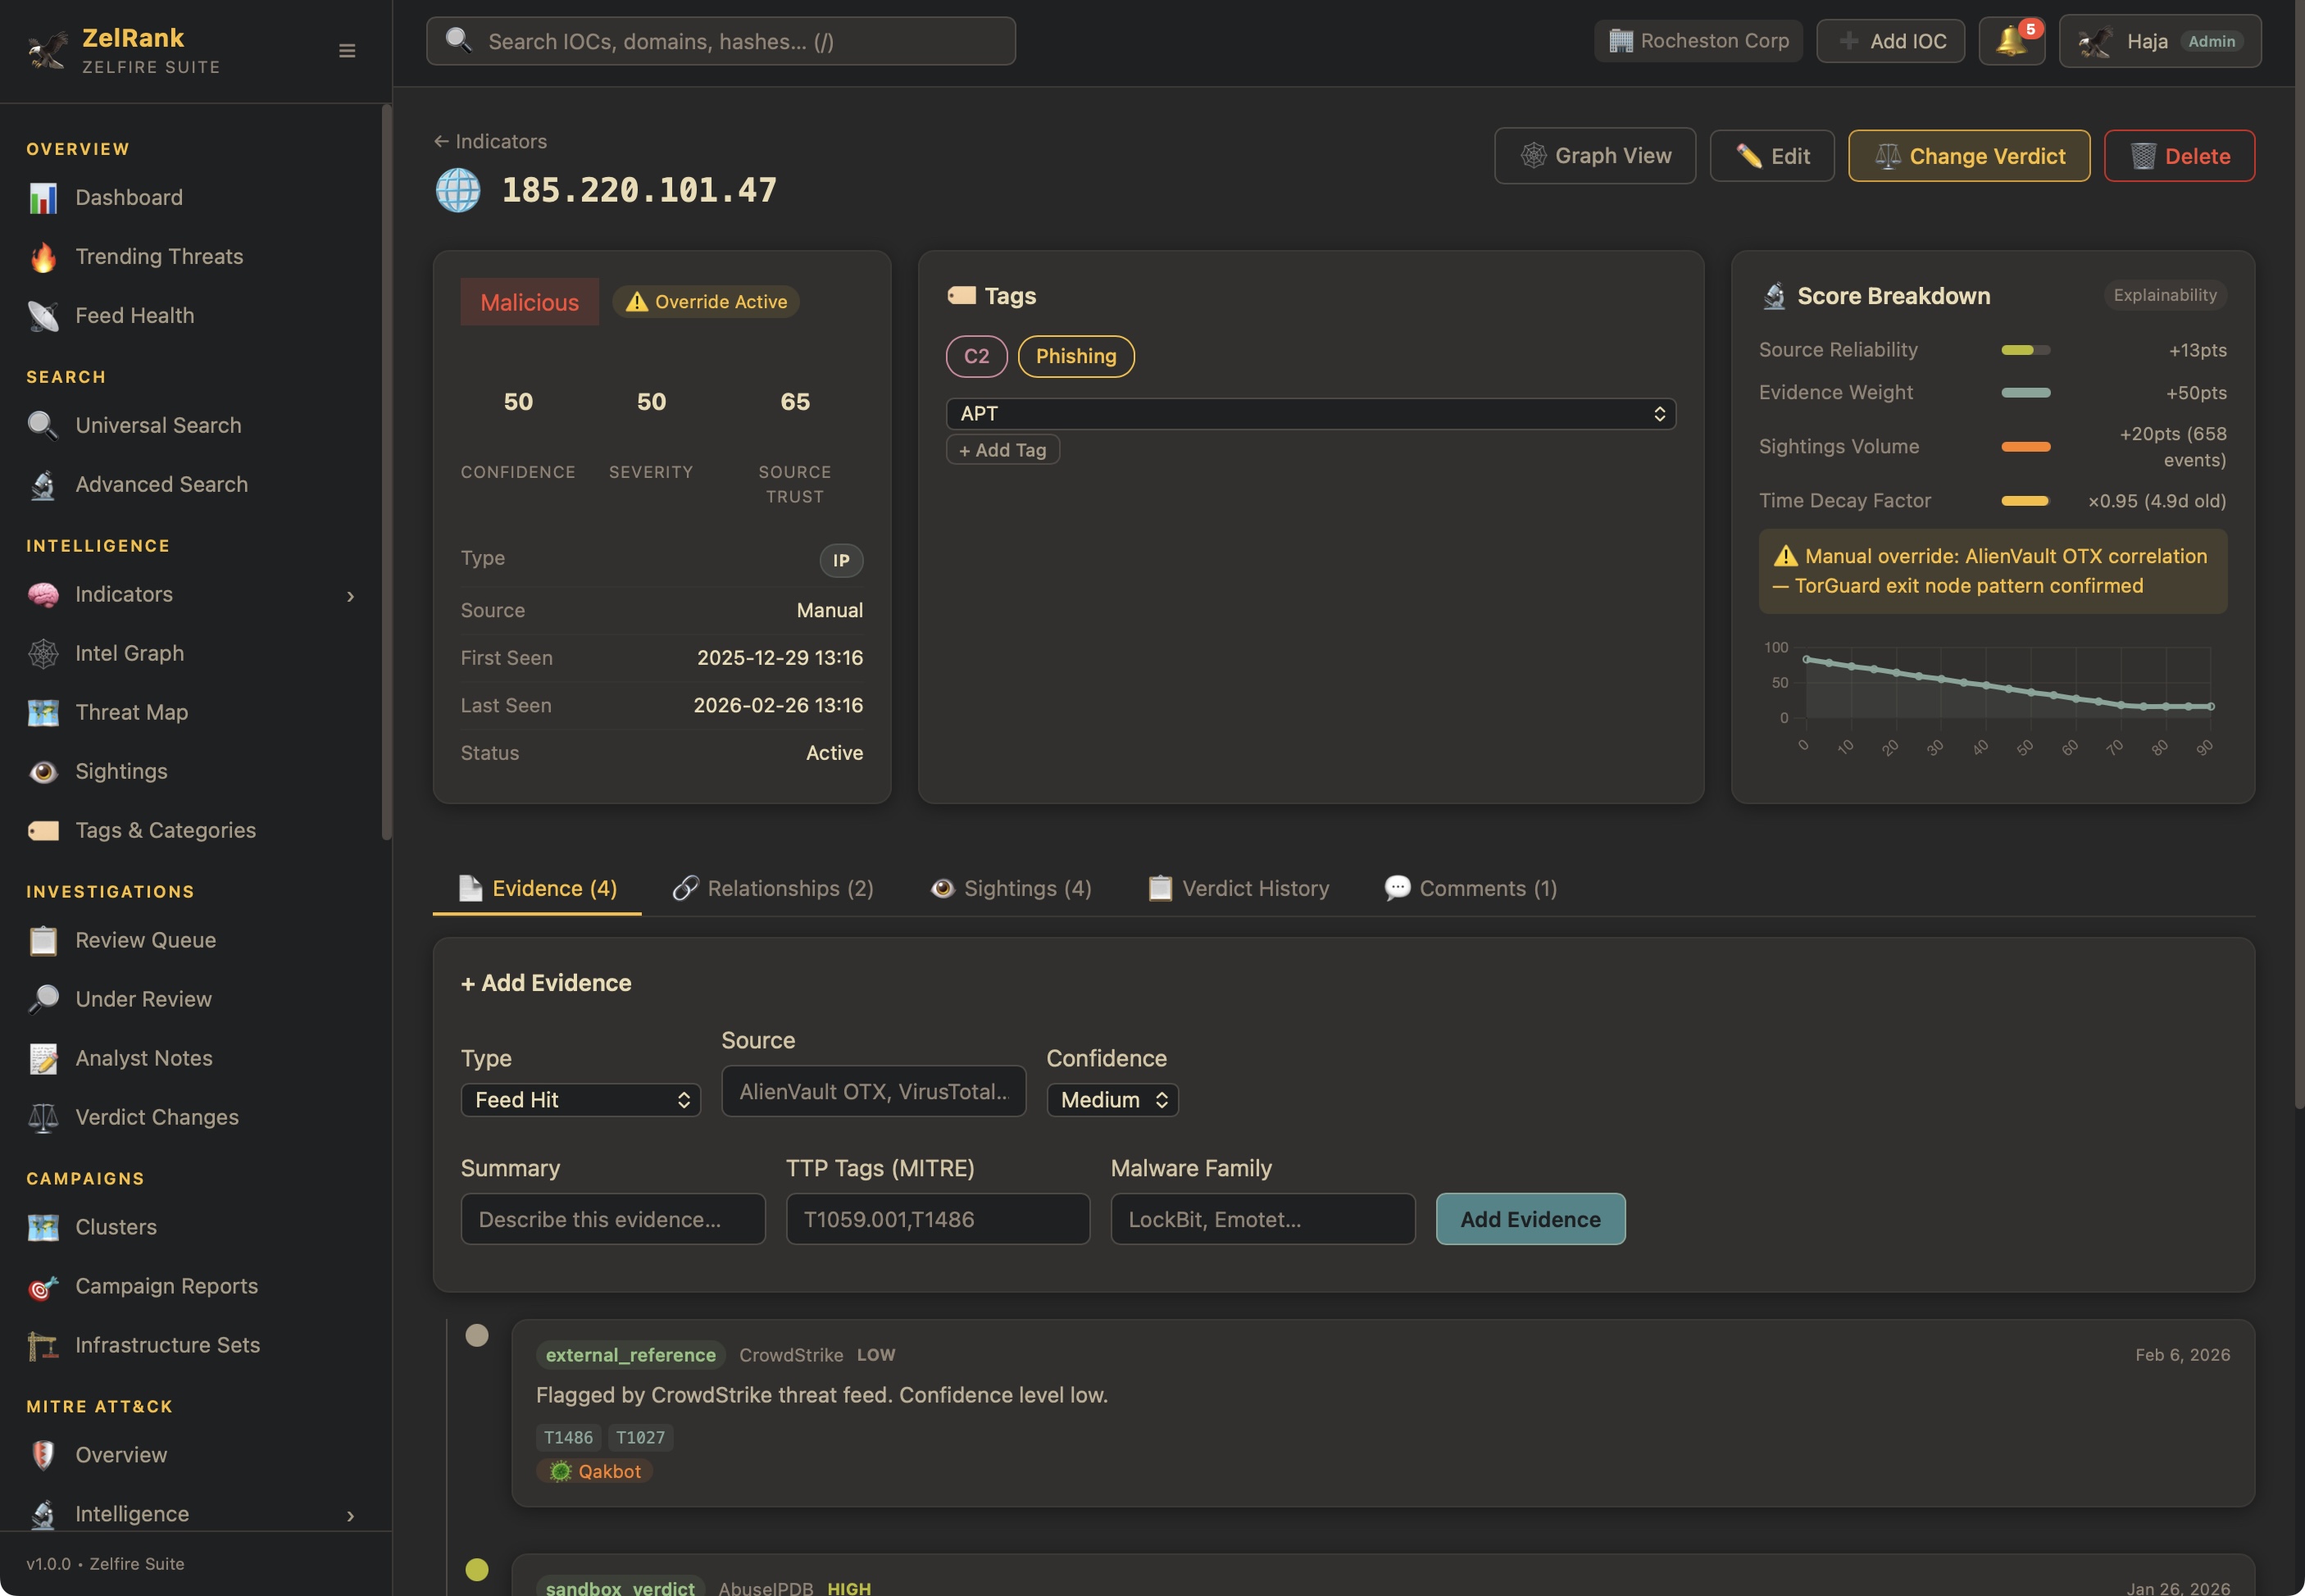
Interactive breakdown of how each indicator’s risk score is calculated with full explainability.
Native integration across ZelXDR, ZelScan, ZelMap, ZelWall, ZelCloud, and ZelSOAR.
Exclusively licensed to RCCE students for hands‑on training with production‑grade CTI capabilities.
Eliminates CTI complexity with structured ingestion, explainable scoring, and seamless integration.
Dashboards, graphs, heatmaps, timelines, and analytics for operational and strategic teams.
Shifts from reactive collection to proactive, AI‑enhanced, explainable intelligence management.
Program automation, AI agents, correlation rules, and scoring behaviors using Rocheston’s ZelC language.
Seamless Zelfire ecosystem integration ensures a synchronized, closed‑loop intelligence workflow.
Embedded in RCCE’s curriculum to teach real‑world CTI operations end‑to‑end.
INSIDE ZELRANK
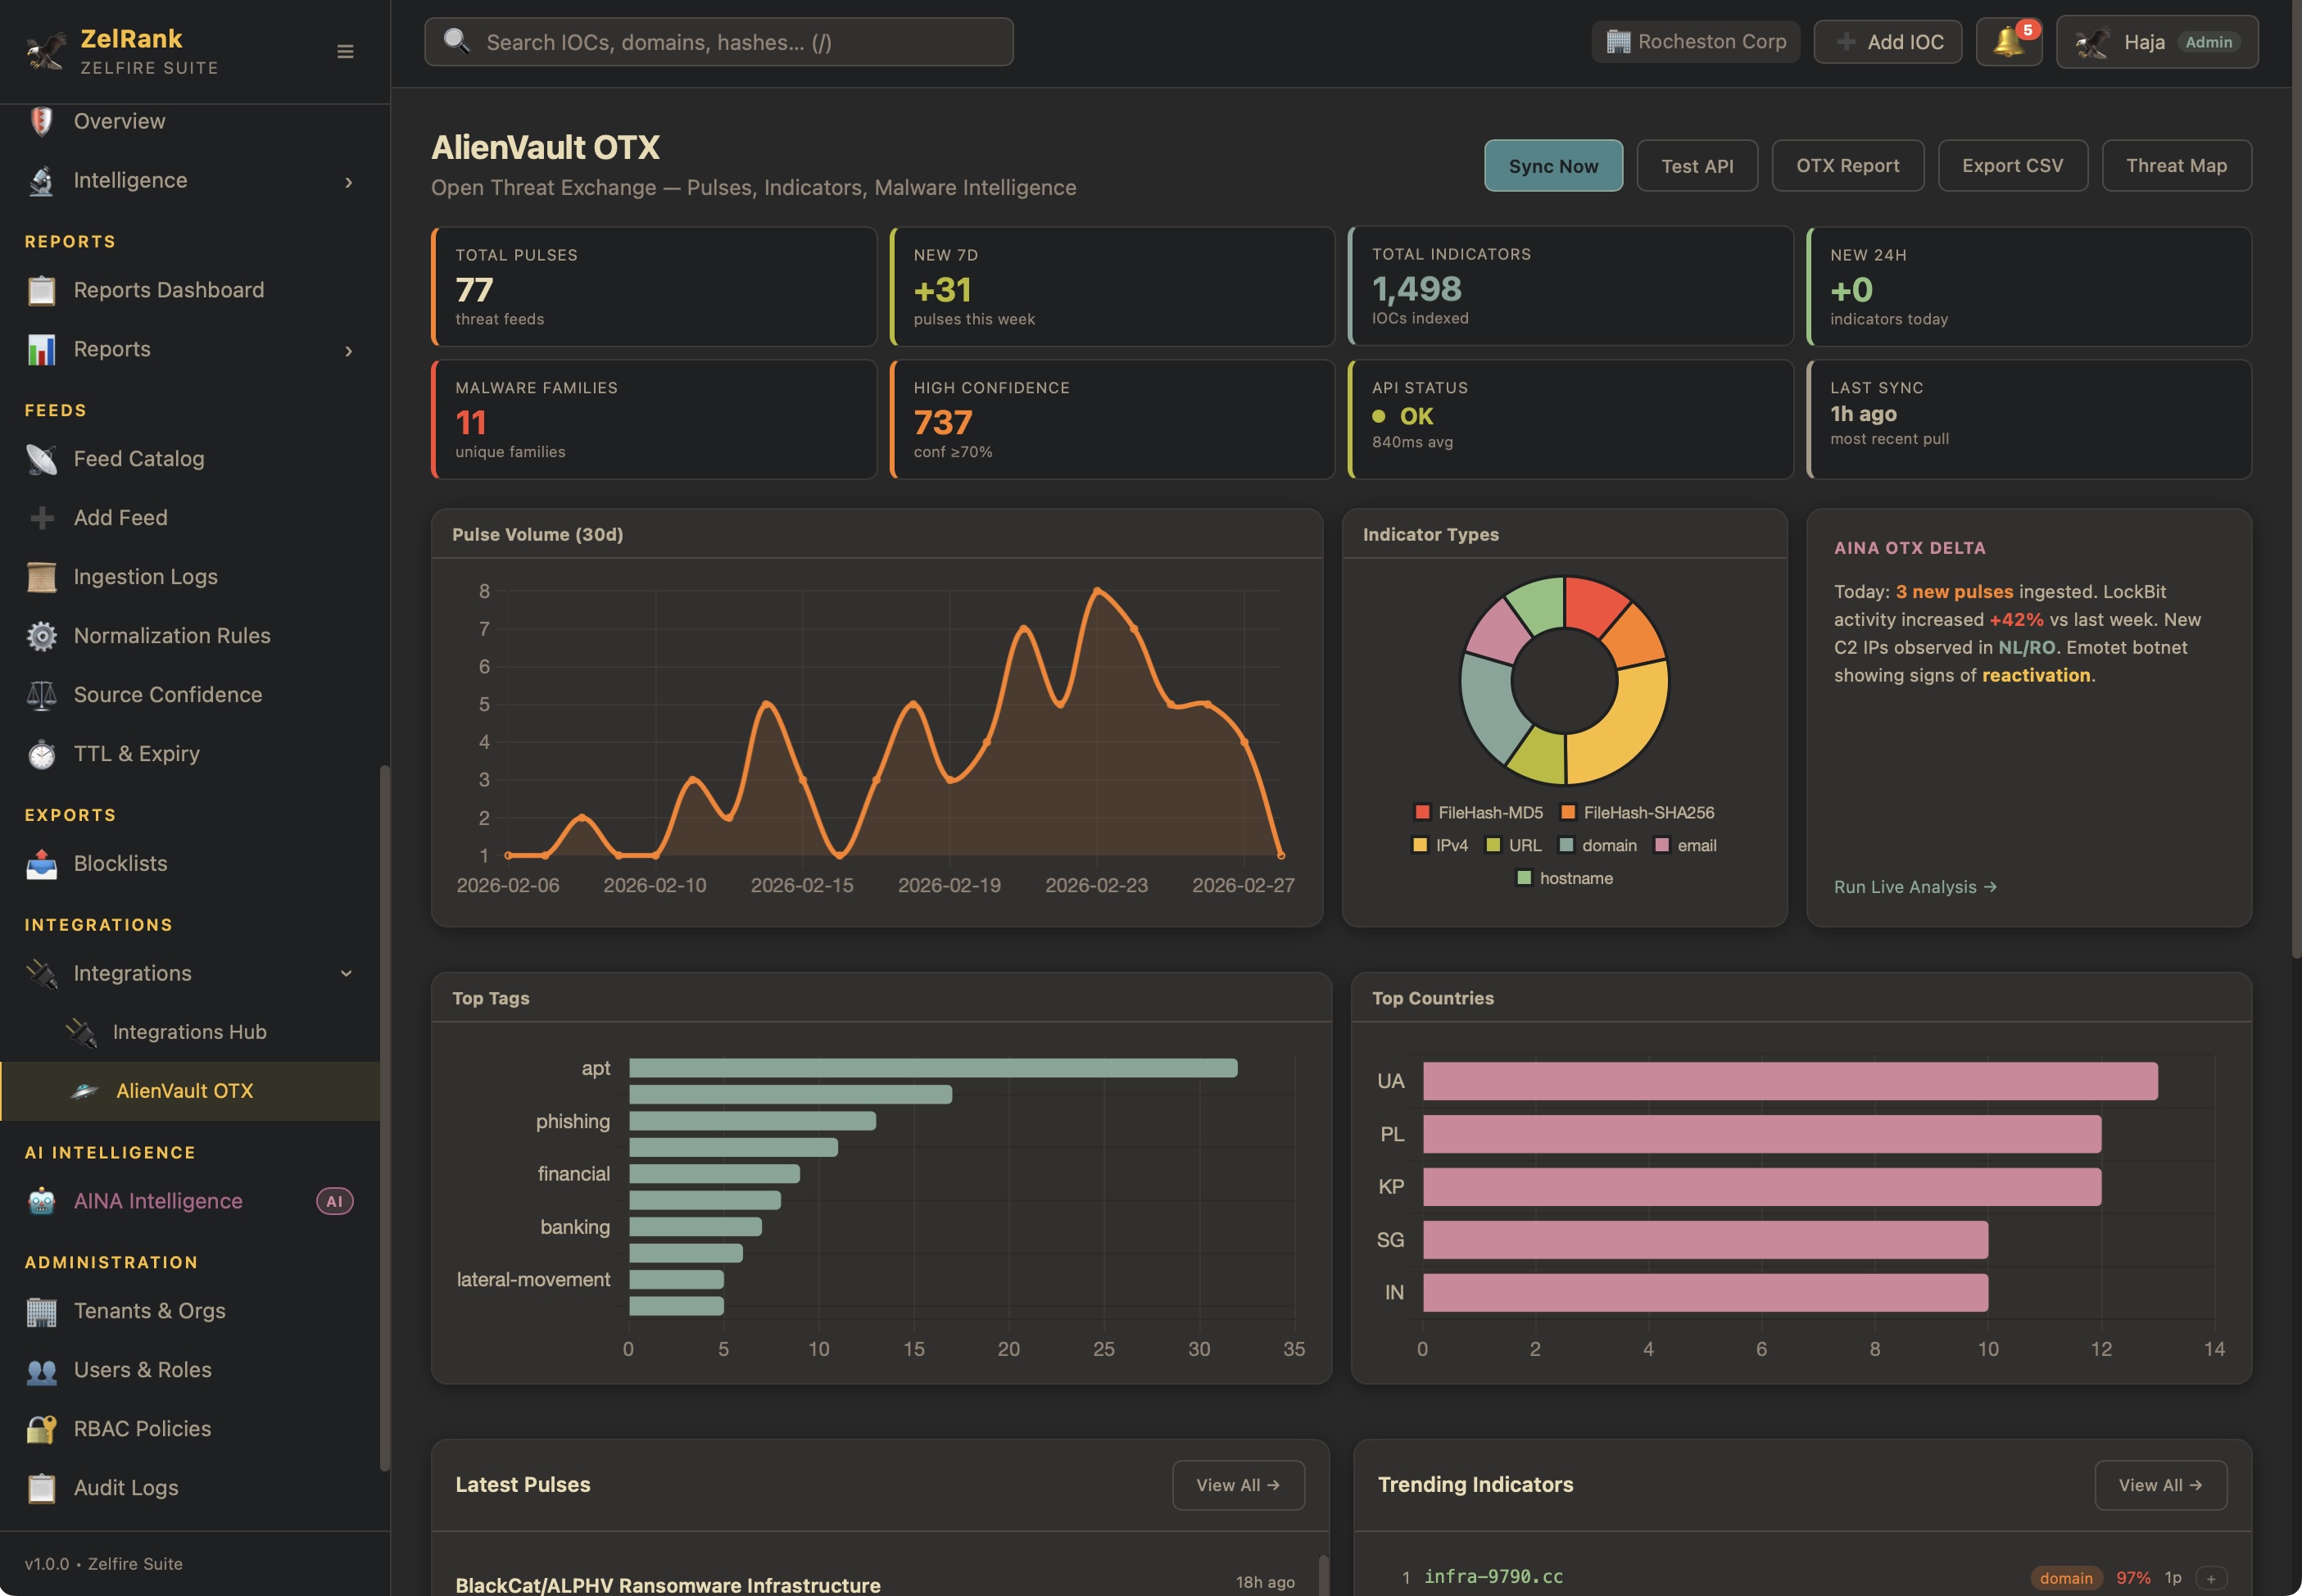
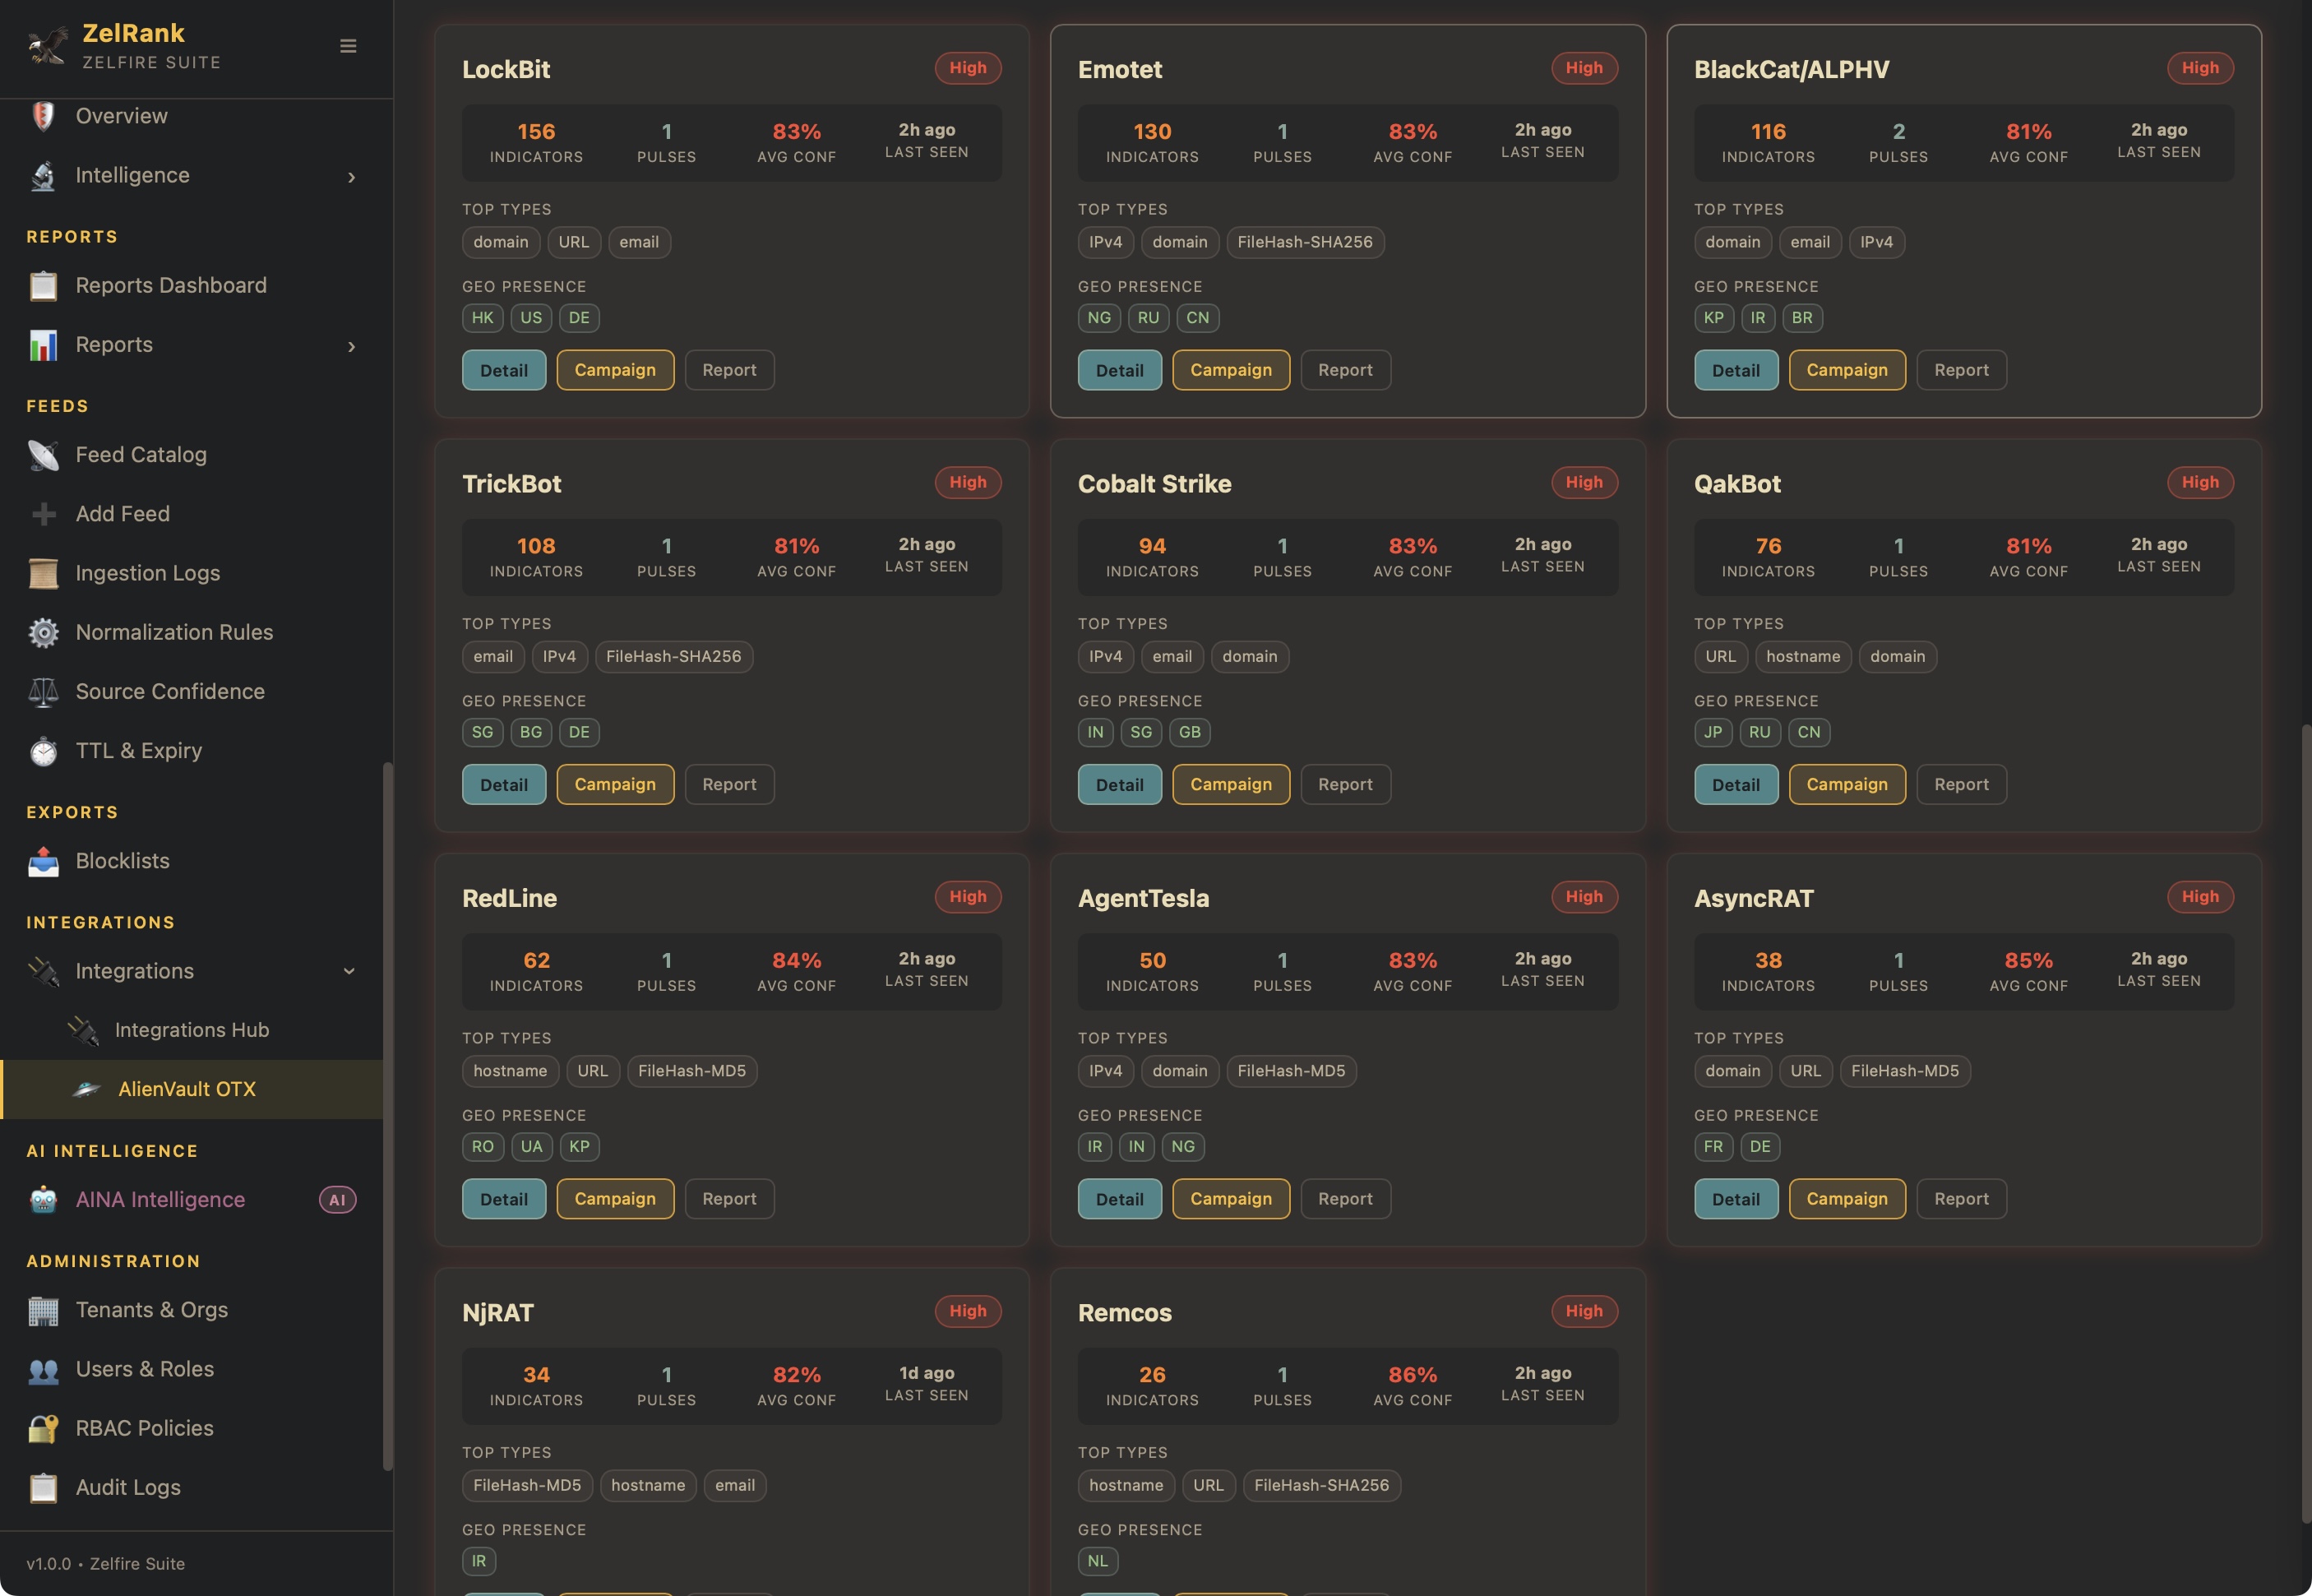
Explore 12 product screenshots. Select any image for a closer look.
THE DETAILS THAT MATTER
Answers about the product, its capabilities, and how it fits into your security workflow.
ZelRank is a next-generation Cyber Threat Intelligence (CTI) platform that collects, normalizes, enriches, correlates, analyzes, visualizes, and operationalizes threat intelligence. It is a core component of the Rocheston Zelfire cybersecurity suite and is powered by AINA, Rocheston’s AI intelligence engine.
No. ZelRank is a full intelligence engine with feed ingestion pipelines, conflict resolution, scoring explainability, clustering, campaign management, infrastructure modeling, MITRE mapping, geo visualization, investigation workflows, AI analysis, and reporting — all within a unified architecture.
Every score is explainable through a breakdown panel.
Yes. A vector-based global Threat Map with geo heatmaps, marker clustering, region breakdown, time playback, and overlays.
Yes. An interactive Intel Relationship Graph for relationships, clustering, pathfinding, infrastructure reuse, and risk flow modeling.
Structured threat operations with lifecycle tracking, infrastructure aggregation, attribution scoring, MITRE mapping, geo spread analysis, and AI summaries.
Automatically or manually grouped related indicators based on relationship density, co‑occurrence, infrastructure overlap, and AI-assisted grouping.
Infrastructure analysis across connectivity density, shared nodes, multi-product detection, evolution timeline, and campaign overlap.
Yes. A structured workspace with linked IOCs, evidence tracking, timeline, graph and MITRE views, AI summaries, risk scoring, and reporting.
Yes. Executive and technical reports, campaign briefs, MITRE coverage, threat map, investigation reports, branding, and exports.
TTL governance with per-indicator and per-feed expiration, auto-expire rules, expiry analytics, and revival workflows.
Yes. Data is isolated by user_id with strict role-based access control: Viewer, Analyst, Senior Analyst, Admin.
Yes. Native integration with ZelXDR, ZelScan, ZelMap, ZelWall, ZelCloud, ZelSOAR, Threat Map, Intel Graph, and AINA.
ZelC is Rocheston’s cybersecurity programming language used to program automation rules, manage AI agents, create correlation logic, customize ingestion, and define scoring adjustments.
Unified ingestion, transparent scoring, AI-assisted analytics, cross-suite integration, enterprise observability, and built-in investigation workflows replace fragmentation and opacity.
Yes. Feed SLA monitoring, conflict resolution engine, audit logging, encryption of API keys, full observability, and structured governance.
Yes. Maps indicator geo distribution, campaign spread, regional risk heatmaps, and country-level intelligence summaries.
Yes. Ingestion runs, verdict changes, TTL updates, AI suggestions, investigation updates, feed modifications, and report generation.
Yes. AINA predicts campaign expansion, infrastructure growth, risk escalation, and emerging clusters.
No. Structured feed management, explainable scoring, native integration, and simplified normalization and conflict resolution remove configuration nightmares.
Rocheston ZelRank is exclusively licensed to RCCE students.
No matching questions. Try another word or clear the search.
Explore how AINA connects intelligence across Zelfire, and find the products that complement your workflow.
Attack surface intelligence
Discover assets, understand exposure, and prioritize the risks that need attention.
Detection & response
Correlate endpoint, network, identity, and cloud signals into a connected incident view.
Response automation
Coordinate response playbooks with approvals, orchestration, and audit trails.
LET’S CONNECT YOUR DEFENSE
Explore the products, see the workflows, and talk to Rocheston about your security environment.
Request a demo